Гласовете на Америка – брой 2

Post Syndicated from Йоанна Елми original https://www.toest.bg/glasovete-na-amerika-broy-2/

Гласовете на Америка – брой 2

Едно време всички баби гледаха сериали. Сигурно още гледат. Но едва сега, като зрял човек, който цени разказването на истории и дори понякога се опитва да го прави, мога да оценя тънкото изкуство на сапунката. 

Половин час гледане на който и да е епизод на сериала стига, за да се запознае човек с всички герои, да отгатне кой каква връзка има с друг, да си избере любимец, да намрази злодеите и да провери в програмата кога е следващият епизод, за да не пропусне развитието. 

Но дори и да се изпусне повече от един епизод, упражнението просто се повтаря, защото такъв е гениалният дизайн на сапунката – верига от циклични микроразкази, които никога не омръзват. Така човек може да не е гледал повече от половината сериал, но да знае точно какво се случва. И дори да предскаже събитията с относителна точност. 

Е, нещо такова е и американската политика. 

Разрив в рая: Тръмп и Мъск 

Последната седмица донесе очакван обрат: двама от главните герои охладняха един към друг и дори си размениха остри реплики. В крайна сметка в никой класически сюжет няма място за двама главни герои, освен ако не са влюбени, разбира се. След като парализира или напълно премахна множество от държавните агенции, които разследваха бизнесите му, милиардерът Илън Мъск обяви, че напуска властта, за да се фокусира върху компаниите си. На разлъка разкритикува проектобюджета на президента Тръмп, наричайки го „гнусно недоразумение“. 

Големият красив законопроект 

Според независимата Бюджетна агенция на Конгреса „Големият красив законопроект“ на президента Тръмп ще увеличи националния дълг с 2,4 трлн. долара. Това може да се окаже проблем за републиканците, за които намаляването на дълга е основен приоритет от години. Естествено, ако допуснем, че е възможно да се мисли извън партийната линия, във факти и реалности, което също е проблем за републиканците. Вече тече активна кампания, според която експертите, позволяващи си волности, като критичност и обективни оценки, лъжат народа и са част от световната конспирация. Отново – предвидимо. На всички е ясно, че са прави само онези експерти, които са съгласни с нас.

Илън Мъск вече подстрекава избирателите да звънят на своите представители, за да стопират законопроекта. Няма как да не го кажа: въпреки че понякога е ужасно глупава, демокрацията все пак продължава да бъде красива. 

Подробна разбивка на спестяванията и разходите, ако законопроектът бъде приет в този вид, може да бъде видяна тук. За потребителите, които не си падат по аргументирани обяснения или „мейнстрийм медии“, ето какво казва изкуственият интелект „Грок“ на Мъск: 

Гласовете на Америка – брой 2

По-малко пари за медицина, повече за крипто, плюс търговски сделки и яйца 

Сред другите постижения на администрацията от последните дни и седмици са над 2500 медицински изследвания с орязано или напълно спряно финансиране. „Хората трябва да знаят, че се спират проучвания, които вероятно биха подкрепили – казва пред „Ню Йорк Таймс“ д-р Идън Танър, химик от Университета в Мисисипи. – Бих искал да открия лечение за рака на мозъка. Не мисля, че в това има нещо кой знае колко скандално.“ 

Трябва да се пестят пари, особено държавни. От началото на президентството си семейство Тръмп е увеличило богатството си с милиарди. Но в крайна сметка не може само да се работи, човек трябва и да си угажда. Президентът до такава степен отговаря на американския идеал за себереализация и уповаване на частния капитал, че дори сам си подсигури самолет. Може обаче да се окаже, че администрацията е поискала самолета от Катар, а не е точно подарък, както съобщиха в началото. Някой може да сметне това за леко awkward или криндж, както казват младите, но всъщност е the art of the deal (от „Изкуството на сделката“ – книгата и слоганът, с който е известен настоящият президент). А президентът и бездруго каза, че този самолет му е прекалено голям. 

Междувременно през април администрацията на Тръмп се закани, че за 90 дни ще сключи 90 търговски сделки с 90 държави – нещо като 800-те дни на Сакскобургготски, но по американски. Дотук е сключена цифром и словом една сделка, но е само юни, а и винаги можем да отхвърлим реалността с аргумента, че мейнстрийм медиите лъжат, и да си измислим друга – докато не се наложи да напазаруваме в магазина, където тази седмица може да няма яйца или когато има, цените да са като за реплики на Фаберже. Но пък баба ви само яйца е яла в миналото, към което Америка трябва да се върне, за да бъде велика отново. Ако нещата стават все по-автентични, значи вървим към успех.* 

Сега сериозно: през април инфлацията се забавя съвсем леко, но непредвидимостта на администрацията не позволява стабилни икономически прогнози, казват експерти. Митата вече се отразяват в повишение на цените на някои стоки, а производителите започват да вдигат цените за крайния потребител. Сред ключовите стоки, които се следят като индикатор за добра икономика и покупателна способност, през май са се вдигнали цените на яйцата, пилешкото, мляното говеждо и портокаловия сок, цената на хляба е стабилна, а беконът леко е поевтинял – като няма яйца, да ядат бекон. 

Има ли последно мита, или няма? 

Заради митата над стоманата се очаква поскъпване на строителните материали и автомобилите. Някои мита остават в сила дори след като съдът се произнесе, че Тръмп може би е превишил правомощията си. Ако човек обаче иска да разбере кои мита точно, трябва да проверява ежедневно. Но ежедневната проверка вече се е превърнала в общ навик, тъй като президентът си мени мнението бързо – все пак е зодия Близнаци, а на 14 юни отбелязваме рождения му ден с първи по рода си военен парад. Освен ако дотогава не реши нещо друго. 

Наясно със ситуацията са само твърдите поддръжници на президента, които също променят мнението си със завидна гъвкавост спрямо актуалните сюжети. Но това може само да предизвика възхита, защото тази вяра издава таланта на Тръмп да прави политика. Или пропаганда. Или пък по малко и от двете. И при латиноамериканските сериали човек рядко помни какво точно е станало в предишния епизод, затова винаги му е интересно. Актуалните социологически проучвания показват около 50% неодобрение и между 46% и 49% одобрение. Кучетата си лаят, сериалът си върви. 

Ало, ало, говори опозицията?

Хубаво е, че американската политика може да разчита на силна, витална опозиция с ясно изграден план за (противо)действие. Това ни разкрива най-малкото заглавие в Newsweek, което гласи: „Колко представители на демократите са умрели от началото на политическия сезон?“ Отговорът е трима, а за позналите правилно има предвидено по едно яйце. Да знаете, че последното си го измислих, защото напоследък ни е трудно да различаваме реалност от нереалност, а и всички са станали ужасно обидчиви. 

Анкета показва, че избирателите на демократите предпочитат популистки послания, като например борба срещу монополите на корпорациите и концентрацията на богатство пред „плановете за изобилие“, вероятно защото не са разбрали какво точно означава последното, което, общо взето, резюмира политическите послания на Демократическата партия. Междувременно много корпорации не празнуват и не подкрепят Месеца на прайда тази година, а данни показват, че американците започват да се усещат, че поставянето на определено знаме върху корпоративното лого и използването на „правилните“ думи и местоимения поради страх от онлайн линч може би не успява да реши нито проблема с равноправието, нито този със свободата. 

А със стоте дни какво стана? 

За домашно от предишния път ни останаха данъчните реформи и цените, които вече засегнахме. В случай че още не сте разбрали за войните в Украйна и Израел, които президентът обеща да прекрати за отрицателно време, в истинския дух на бавните новини и на мисията на „Тоест“ ще ви съобщя, че и двете все още продължават. 

Президентът Тръмп обяви, че Путин му съобщил, че ще отмъсти на Украйна за атаките в края на май, които унищожиха значителна част от руските ядрени бомбардировачи и ще останат в историите като една от най-впечатляващите военни операции. Добре, Владимир, изглежда е казал президентът Тръмп, защото обществото не научи повече. Вероятно се разбират добре, защото Путин има Луна в Близнаци; в следващ бюлетин може да предложим и синастрия.

Не че американският президент се слави с пословично търпение – екипът му обмисля да му прави брифинги като риалити шоу, защото хич не обичал да чете – но агресивната кампания по изтребването на населението на Газа зад паравана на антитероризма явно вече е неудобна дори на САЩ, защото в последните седмици се наблюдава охладняване в отношенията с Израел и лека смяна на тона, което не попречи на САЩ да наложат ново вето в ООН. Разбира се, по-вероятната причина е промяна в политиката на страната спрямо Иран и цялостното преориентиране на ролята на Америка в Близкия изток, където Тръмп наскоро държа съвсем нелоша реч със заявки за промяна във външната политика в региона, което има потенциал да бъде част от конструктивно наследство. Такъв потенциал имаха и редица други политики на Тръмп, но както винаги, изпълнението е по-сложна работа.

А на образованието ще посветим следващия брой. 

* Гласът на миналото и обяснителна журналистика за едно яйце 

Споменаваме яйцата полуиронично, защото са политическа басня с поука и добра илюстрация за настоящия политически и медиен климат. 

Цената на яйцата се превърна в тема през последните месеци на президентската кампания, когато Джо Байдън все още беше на власт, въпреки че определянето на цените няма нищо общо с това кой е президент, а се влияе от много по-сложни фактори. 

Тръмп обеща 50% спад на цената на яйцата, но въпреки тези обещания тя достигна рекордни нива. В началото на май прорепубликанската Fox News публикува материал със заглавие „Цената на яйцата е спаднала с 61% от началото на управлението на Тръмп“. Отвъд заглавието обаче става ясно, че понижението на пазарните цени е в резултат на „слабото търсене и спад на случаите на птичи грип“, както и на внос от Турция, Бразилия и Южна Корея плюс уравновесяване между цените на едро и пазарните цени. Статията на Fox не казва каква конкретно е ролята на президента за промените в пазара, защото както Джо Байдън, така и Тръмп няма никаква власт над яйцата (което би било добра идея за герой на Marvel или DC). От другата страна пък демократите също опитаха да извлекат политически дивидент от яйцата, например с отворено писмо до Тръмп, а много медии използваха случая за провокативни заглавия, които да хвърлят по някое виртуално яйце към президента. 

Яйца за всички, навсякъде, наведнъж.

И разбира се, поантата – от януари насам президентът Тръмп повтаря, че цените на яйцата падат. Заглавието на CNN резюмира финала на баснята (и политическата стратегия на Тръмп) най-добре: „Фикцията на Тръмп става реалност“. Бих добавила едно „в редки случаи“. Този път за доброто на потребителя. 

Останалото е просто зрелището на политиката, което трябва да понасяме спокойно, с критична мисъл, и както в този случай – с щипка хумор. 
Гласовете на Америка – брой 2
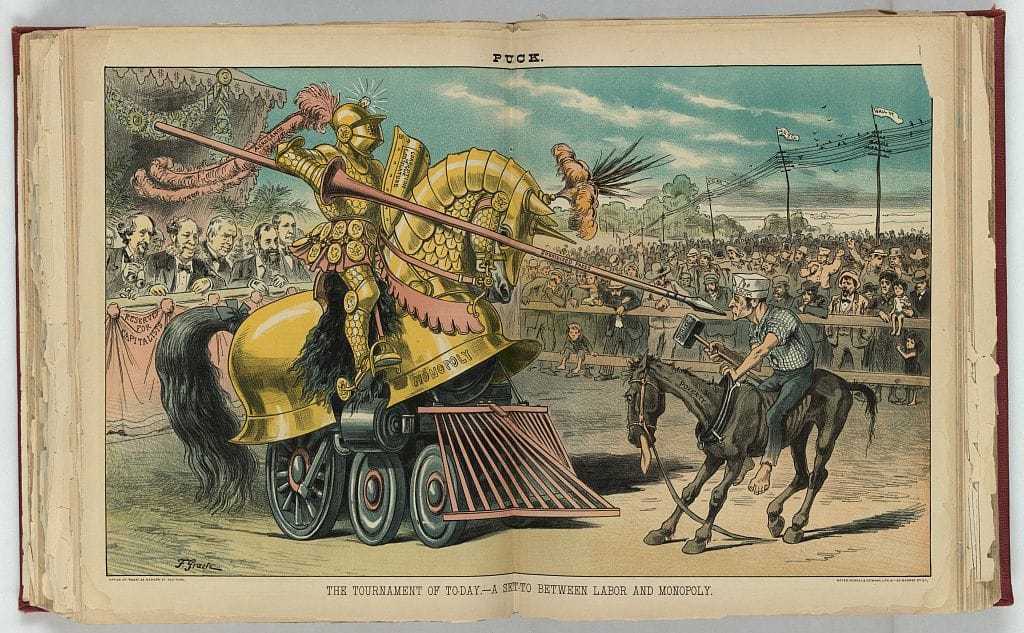
Ф. Грец, от колекцията на Библиотеката на Конгреса

Карикатурата изобразява схватка между огромен рицар на златен кон с надпис „Монопол“. Върху перото на шлема му пише „арогантност“, върху щита – „корумпирано законодателство“, а върху копието – „субсидирана преса“. Босият му опонент работник язди „бедността“ и държи в ръката чук с надпис „стачка“. Местата вляво са „запазени за капиталисти“, а между тях виждаме Уилям Вандербилт и Джон Роуч, магнати от т.нар. Позлатена епоха, период на висока концентрация на богатство и огромни неравенства от историята на САЩ. 


Абонирайте се, за да получавате този бюлетин на електронната си поща в момента, в който излезе!

Вече сте регистриран потребител на Toest.bg? Може директно от настройките на бюлетините в своя профил да изберете „Гласовете на Америка“ или да натиснете бутона по-долу:

Още нямате профил в Toest.bg? Регистрирайте се само с няколко клика:

India’s cyber leaders prepare for AI-driven threats

Post Syndicated from Rapid7 original https://blog.rapid7.com/2025/06/06/indias-cyber-leaders-prepare-for-ai-driven-threats/

India's cyber leaders prepare for AI-driven threats

As India’s economy rapidly digitizes, cybersecurity challenges are becoming increasingly complex. This May, Rapid7 launched our inaugural Global Security Day series across India, bringing together top security leaders in Mumbai, Delhi, and Bengaluru to address the most pressing cyber threats facing organizations in 2025.

Key insights that emerged

Across all three cities, several critical themes emerged that are shaping India’s cybersecurity landscape:

AI is No Longer Optional: Organizations recognize that AI has become essential for threat detection, exposure management, and SOC operations. The question is no longer whether to adopt AI, but how to implement it effectively.

Attack Surface Explosion: Cloud misconfigurations, insecure APIs, and identity misuse are driving today’s biggest risks. Organizations are struggling to maintain visibility and control across increasingly complex environments.

SOC Modernization is Urgent: Traditional Security Operations Centers need fundamental transformation, with automation and AI at their core to handle the volume of modern threats.

Talent Gap Challenges: Upskilling and reskilling initiatives are critical to closing the cybersecurity talent gap that’s affecting organizations globally, but particularly acutely in India’s booming tech sector.

Regulatory Evolution: India’s evolving cybersecurity regulatory landscape is shaping how organizations approach their security investments and strategy development.

A journey across India’s cyber capital cities

Our three-city roadshow, organized in collaboration with Information Security Media Group (ISMG), focused on the theme “2025 Cyber Threat Predictions: AI-Driven Attacks, Ransomware Evolution, and Expanding Attack Surface.” The response from India’s cybersecurity community was overwhelming, with 138 security leaders and delegates participating across all three cities.

Launching with impact in Mumbai (May 8)

Our Mumbai kickoff set the tone for the entire series, drawing 43 security leaders eager to dive into critical cybersecurity challenges. Rob Dooley, General Manager APJ, welcomed attendees before Regional CTO Robin Long delivered comprehensive insights on:

  • Global and Asia-Pacific threat landscape trends
  • The evolution of ransomware from double extortion to hybrid attacks
  • Expanding attack surfaces driven by cloud misconfigurations and insecure APIs
  • Next-generation defense strategies leveraging AI and continuous threat exposure management (CTEM)

The highlight was our fireside chat featuring Starlin Ponpandy, CISO of Orion Systems and Rapid7 customer, discussing ‘Building a New-Age SOC: Practical Applications of AI’. The conversation explored choosing the right SOC model, building effective teams, and navigating the complexities of AI trust and explainability.

The main focus of the Q&A was the evolving cyber threat landscape and how organizations can prepare for 2025’s AI-driven, increasingly complex attack environment.

The conversation was dominated by leaders sharing insights on the rise of AI-powered threats, the shift in ransomware tactics to double and hybrid extortion and the urgent need for proactive threat exposure management. Rapid7’s emphasis on real-time, AI-enabled defenses and automated risk management strategies sparked strong engagement.

Strategic dialogue in Delhi (May 13)

Our Delhi event brought together 43 delegates for candid, strategic discussions about 2025’s top cyber threats. Security leaders engaged in deep conversations about AI-powered detection and defense, proactive exposure management, and building resilient SOCs with automation.

The panel discussion on ‘Building a New-Age SOC’ addressed critical challenges including the cybersecurity talent gap and integrating security into DevOps workflows, a thought-provoking conversation examining identity-centric security models and the shift from traditional SOCs to Managed Detection and Response solutions.

Attendees posed incisive questions about upskilling teams in an AI-driven environment, managing tool sprawl, and operationalizing security by design – highlighting the sophisticated thinking of India’s cybersecurity leadership.

Tactical discussions in India’s Silicon Valley – Bengaluru (May 15)

Our Bengaluru finale drew the largest crowd with 52 delegates, including CISOs and cybersecurity executives from across South India. The discussions were highly tactical, focusing on:

  • Modernizing SOCs through AI-led threat detection
  • Countering double and triple extortion ransomware
  • Risk automation and secure cloud transformation

Veteran industry speaker Satish Kumar Dwibhashi joined Robin Long for discussions that reinforced a clear theme: security strategy must evolve in lockstep with attacker innovation.

Building for the future

The success of our India Security Days reflects not just the hunger for cybersecurity knowledge in the region, but also Rapid7’s commitment to supporting India’s digital transformation journey. We’re excited to announce that we’re expanding our presence with aGlobal Capability Center (GCC) in Pune, which will serve as a hub for innovation and home to teams across engineering, business support, and our Security Operations Center (SOC).

This initiative represents more than just business expansion – it’s about building cybersecurity capability and expertise right here in India, that will shape a secure digital future for organizations around the world.

The road ahead

The conversations, connections, and insights from our India Security Days have reinforced our belief that India’s cybersecurity community is among the most forward-thinking globally. The challenges are significant – from AI-powered attacks to evolving ransomware tactics – but so is the talent, innovation, and determination to address them.

As we look toward 2025 and beyond, events like these remind us that cybersecurity is ultimately about people: the security leaders making tough decisions, the practitioners implementing defenses, and the communities sharing knowledge and supporting each other.

Thank you to all the security leaders who joined us in Mumbai, Delhi, and Bengaluru. Your engagement, questions, and insights made these events truly impactful. We look forward to continuing these conversations and supporting India’s cybersecurity community as we navigate the challenges and opportunities ahead.

Interested in joining our growing team in India? Learn more about career opportunities at our new GCC in Pune.

Access Claude Sonnet 4 in Amazon Q Developer CLI

Post Syndicated from Kirankumar Chandrashekar original https://aws.amazon.com/blogs/devops/access-claude-sonnet-4-in-amazon-q-developer-cli/

Amazon Q Developer now supports Claude Sonnet 4 within the CLI, bringing advanced coding and reasoning capabilities to your development workflows at no additional cost. This latest model excels in coding with a state-of-the-art 72.7% for agentic coding on the SWE-bench (see Claude 4 announcement for more information). With enhanced coding and reasoning capabilities, it helps you analyze complex code, optimize everyday development tasks, implementing bug fixes, running bash commands, and developing new features with immediate feedback loops and more precise responses.

To help you leverage Claude Sonnet 4, Amazon Q Developer lets you easily select specific Claude Sonnet models, giving you increased flexibility the CLI.

  • Claude Sonnet 4: High-performance model with balanced intelligence
  • Claude Sonnet 3.7: High-performance model with extended thinking capability
  • Claude Sonnet 3.5: High-performance intelligent model

For detailed information about Claude model capabilities and comparison, refer to the Anthropic models overview.

In this blog, I will show you how to select Claude Sonnet 4 as your model within the Q Developer CLI and then walk you through a quick demo.

How to Choose Claude Sonnet 4

Make sure to update to the latest version (v1.11.0 onwards) of Amazon Q Developer CLI. Refer installing Amazon Q for command line for installation instructions. You can access Claude Sonnet 4 through these options:

  • During an active chat, use the /model command and select claude-4-sonnet
  • Start a new chat with q chat --model claude-4-sonnet
  • Set it as your default model using q settings chat.defaultModel claude-4-sonnet.

The supported model names for the --model parameter and settings are:

  • claude-3.5-sonnet
  • claude-3.7-sonnet (default)
  • claude-4-sonnet

Model Selection Priority Order

Q Developer CLI selects models in the following order:

  1. Current session model selections (via /model or --model)
  2. User-configured preferences in settings
  3. System default (Claude 3.7 Sonnet)

Key Behaviors

The Q Developer CLI agent defaults to Claude 3.7 Sonnet when no specific model is selected. During active chat sessions, you can seamlessly switch between models using the /model command. Chat continuity is maintained across sessions, with the system retaining the previously selected model when conversations are resumed. If you prefer Claude Sonnet 4, setting it as the default model in user settings will automatically apply to all new chat sessions, though this can be overridden with specific model selections as needed.

qcli-model-selection

Figure 1: Q Developer CLI showing the model loaded for the session

Claude Sonnet 4 with Q Developer CLI in Action

After switching to Claude Sonnet 4 in Q Developer CLI, let’s explore its capabilities with a practical coding example. Here’s the prompt I’ll use for this demonstration:

Create a Python command-line to-do list app with these features:
- Add tasks with descriptions and priorities (low/medium/high)
- Mark tasks as complete by index
- Display tasks sorted by priority, then insertion order
- Show completion status ([x] done, [ ] pending)
- Handle errors for empty tasks and invalid indices
- Store tasks in memory only
Please provide the code to implement this application.

qcli-model-selection-claude-sonnet-in-action

Figure 2: Q Developer CLI interface showing Claude Sonnet 4 in action

In the above demonstration, Q Developer CLI with Claude Sonnet 4 went beyond what was asked in the provided requirements in the prompt by implementing sophisticated command parsing with quoted descriptions, comprehensive error handling, and clean object-oriented design enhanced by type hints. The interface features a helpful guidance system with clear error messages, elegant enum-based priority management, and formatted output for clear task representation.

Additionally, Q Developer CLI with Claude Sonnet 4 also generated documentation in the README for the to-do application, including practical error handling examples and clear usage instructions – transforming the prompt requirements into a well-structured, user-friendly application.

Conclusion

The availability of Claude Sonnet 4 represents a significant advancement in Amazon Q Developer’s capabilities. From intricate code refactoring to streamlined documentation creation, Claude Sonnet 4 helps you accomplish both complex and routine development tasks efficiently.

Whether selecting Claude Sonnet 4 for complex tasks or using other models for specific needs, Amazon Q Developer adapts to your preferences, optimizing AI assistance while maintaining efficiency in your workflow.

The latest version(v1.11.0) of Amazon Q Developer awaits in the CLI, ready to support your development journey with enhanced model capabilities and selection options. Refer Installing Amazon Q for Command line for installation instructions.

To learn more about Amazon Q Developer’s features and pricing details, visit the Amazon Q Developer product page.

About the Author

kirankumar.jpeg

Kirankumar Chandrashekar is a Generative AI Specialist Solutions Architect at AWS, focusing on Amazon Q Developer. Bringing deep expertise in AWS cloud services, DevOps, modernization, and infrastructure as code, he helps customers enhance their development workflows using Amazon Q Developer. Kirankumar is passionate about solving complex customer challenges and enjoys music, cooking, and traveling.

Now open – AWS Asia Pacific (Taipei) Region

Post Syndicated from Betty Zheng (郑予彬) original https://aws.amazon.com/blogs/aws/now-open-aws-asia-pacific-taipei-region/

Today, Amazon Web Services (AWS) announced that AWS Asia Pacific (Taipei) Region is generally available with three Availability Zones and Region code ap-east-2. The new Region brings AWS infrastructure and services closer to customers in Taiwan.

Skyline of Taipei including the Taipei 101 building

Skyline of Taipei including the Taipei 101 building

As the first infrastructure Region in Taipei and the fifteenth Region in Asia Pacific, the new Region expands the AWS global footprint to 117 Availability Zones across 37 geographic Regions worldwide. The new AWS Region will help developers, startups, and enterprises, as well as education, entertainment, financial services, healthcare, manufacturing, and nonprofit organizations run their applications and serve end users while maintaining data residency in Taiwan.

AWS in Taiwan

AWS has maintained a presence in Taiwan for more than a decade, starting with the opening of the AWS Taipei office in 2014. Since then, AWS has introduced many infrastructure offerings in Taiwan including:

In 2014, AWS launched the first Amazon CloudFront edge location and added another in 2018, offering customers a secure and efficient content delivery network for accelerating data, video, application, and API delivery worldwide.

In 2018, AWS established two AWS Direct Connect locations in Taiwan to enhance connectivity options. With the launch of the AWS Asia Pacific (Taipei) Region, we’ve added a new Direct Connect location in Taiwan to provide customers with higher speed and bandwidth.

In 2020, AWS launched AWS Outposts in Taiwan, helping customers seamlessly extend AWS infrastructure and services to their on-premises or edge locations for a consistent hybrid experience.

In 2022, AWS launched AWS Local Zone in Taipei to support low-latency applications requiring single-digit millisecond responsiveness.

Today, with the launch of the AWS Asia Pacific (Taipei) Region, we further strengthen our commitment to support innovation in Taiwan. Organizations in regulated industries will be able to store data locally while maintaining complete control over data location and movement. From high-tech manufacturing to semiconductor companies and small and medium enterprises (SMEs), businesses will gain access to the scalable infrastructure needed for growth and innovation.

AWS customers in Taiwan

Organizations across Taiwan are already using AWS to innovate and deliver differentiated experiences to their customers, for example:

Cathay Financial Holdings (CFH) is a leader in financial technology in Taiwan. It continuously introduces the latest technology to create a full-scenario financial service ecosystem. Since 2021, CFH has built a cloud environment on AWS that strengthens its security control and meets compliance requirements.

“Cathay Financial Holdings will continue to accelerate digital transformation in the industry, also improve the stability, security, timeliness, and scalability of our financial services,” said Marcus Yao, senior executive vice president of CFH. “With the new AWS Region in Taiwan, CFH is expected to provide customers with even more diverse and convenient financial services.”

Gamania Group is revolutionizing the entertainment landscape by integrating AI with celebrity IP through their innovative Vyin AI platform. Gamania utilized the robust and scalable infrastructure of AWS to develop secure, responsive AI interactions.

Benjamin Chen, chief strategy officer and head of Innovation Lab, said: “The core goal of Vyin AI is to create a digital identity that is fully interactive, lifelike, and safe to use. This demands technologies that are stable, responsive, and secure. To that end, we rely on the robust and resilient cloud infrastructure of AWS, and look forward to the low-latency advantages offered by the AWS Region in Taiwan. AWS provides a highly stable and secure environment for Vyin AI to provide users with secure and AI hallucination free interactions. AWS Cloud services allow us to focus more on core AI technology innovation and the enhancement of the ‘hyper-personalized interactive’ user experience, thereby accelerating product iteration and optimization.”

Chunghwa Telecom is a leader in cloud network services in Taiwan with the broadest mainstream 5G bandwidth, exceptional network speed, and globally recognized mobile internet capabilities. Chunghwa Telecom utilizes generative AI platforms such as Amazon Bedrock to build innovative services and create intelligent applications for various industries.

Dr. Rong-Shy Lin, president of CHT, stated: “With the launch of the AWS Region in Taiwan, CHT’s partnership with AWS has entered a new phase. We will deepen the integration of key advantages of the AWS Region, such as low latency and local data storage, combining them with CHT’s extensive backbone network, rich cloud experience, and professional team that has obtained multiple AWS Competency certifications. This will allow CHT to provide solutions that meet strict security and compliance requirements for government, financial, critical infrastructure, and highly regulated industries. At the same time, we are utilizing AWS technologies such as Amazon Bedrock to develop innovative applications and accelerate digital transformation and AI adoption. We will continue to provide optimized cloud and network services in Taiwan while supporting customers’ global expansion.”

AWS Partners in Taiwan

The AWS Partner Network in Taiwan plays a crucial role in helping customers adopt cloud technologies and maximize value from the new AWS Asia Pacific (Taipei) Region. These specialized partners combine deep technical expertise with local market knowledge to accelerate digital transformation across industries.

eCloudvalley Digital Technology Group is an AWS Premier Tier Services Partner with a team of cloud experts with more than 600 certifications.

“eCloudvalley Group has always embraced our mission of being a cloud evangelist, driving the adoption of cloud technology across Taiwan’s industries,” said MP Tsai, chairman of eCloudvalley Group. “With over a decade of close collaboration with AWS, we are honored to help more and more customers and industries move to the cloud while being part of customers’ digital transformation journey on AWS. We believe that the launch of the AWS Asia Pacific (Taipei) Region will further support Taiwan companies’ digital transformation and innovation in Taiwan with its world-leading cloud technology, while industries with higher local data residency requirements, such as finance and healthcare, will be able to further advance their cloud transformation journey.”

Nextlink Technology Inc. is an AWS Premier Consulting Partner, certified Managed Service Provider (MSP) and has AWS Level 1 Managed Security Service Provider (MSSP) and Government Consulting Competency.

“The investment of AWS in local infrastructure will help drive the digital transformation of Taiwan companies, boosting the development of various industries spanning from traditional industries to emerging digital sectors,” said Shasta Ho, the CEO of Nextlink Technology Inc. “We look forward to continuing working with AWS to help enterprises across industries deeply utilize the new AWS Asia Pacific (Taipei) Region. This local advantage will address customer needs in data localization, low latency, compliance, and high performance computing workloads. We also look forward to using AWS world-leading cloud technologies to power customers’ digital transformation journeys while contributing to the diversification of Taiwan’s economy.”

SAP has been a strategic partner of AWS for more than a decade, with thousands of enterprise customers worldwide running their SAP workloads on AWS.

“SAP is thrilled to see AWS establish new data centers in Taiwan,” said George Chen, SAP global vice president and managing director for Taiwan, Hong Kong, and Macau. “This investment provides Taiwan enterprises with greater choice, lower service latency, and enhanced operational flexibility. As a long-term strategic partner, SAP is committed to accelerating cloud transformation for these businesses. Through RISE with SAP, we can help customers seamlessly migrate to the cloud, enjoying greater flexibility, scalability, and reduced operational costs. By combining SAP’s enterprise solutions with the robust cloud platform of AWS, we’ll jointly empower Taiwan’s enterprises to unlock innovative AI applications and run their core businesses securely and reliably locally, driving Taiwan enterprise cloud transformation together.”

Supporting sustainable innovation in Taiwan

As Taiwan progresses toward its goal of net-zero emissions by 2050, AWS Cloud solutions are empowering organizations to enhance operational efficiency while reducing environmental impact. The new AWS Asia Pacific (Taipei) Region incorporates the AWS commitment to sustainability, helping organizations meet both technical and environmental objectives.

Ace Energy is a pioneer in Taiwan’s energy management sector. Since 2013, Ace Energy has been using AWS services such as Amazon Simple Storage Service (Amazon S3), Amazon Elastic Compute Cloud (Amazon EC2), and AWS IoT Core to provide innovative energy solutions through their Energy Saving Performance Contract model. Ace Energy has deployed energy management solutions across 1,000 locations, helped a semiconductor manufacturer reduce steam consumption by 65 percent, achieved 22 million new Taiwan dollars in annual energy savings, and decreased carbon emissions by 8,000 tons through their waste heat recovery technology.

Taiwan Power Company (Taipower) is Taiwan’s state power utility and has revolutionized its operations through AWS since 2018. By implementing smart grid technologies with drones, robotics, and virtual reality for smart patrol, Taipower has enhanced customer experience through the “Taiwan Power” application. The company has improved operational efficiency through data-driven decision-making and earned six consecutive Platinum Awards in the Corporate Sustainability category at the Taiwan Corporate Sustainability Awards.

Building cloud skills together

Since 2014, AWS has built comprehensive programs for cloud education and skills development in Taiwan. For example, educational programs such as AWS Academy, AWS Educate, and AWS Skill Builder have helped train more than 200,000 people in Taiwan on cloud skills. These programs will expand alongside our infrastructure investments to build a foundation for Taiwan’s digital future.

Taiwan boasts a vibrant AWS community that welcomes your involvement. Take part in knowledge-sharing and networking at local AWS User Groups in Taipei, engage with the four celebrated AWS Heroes in Taiwan, or consider becoming part of the growing community of AWS enthusiasts by joining the ranks of the 17 AWS Community Builders already contributing to Taiwan’s cloud ecosystem. All these community connections provide valuable opportunities to accelerate your cloud journey through local expertise and collaborative learning.

Stay tuned
The AWS Asia Pacific (Taipei) Region is ready to support your business. You can find a detailed list of the services available in this Region on the AWS Services by Region page. For news about AWS Region openings, check out the Regional news of the AWS News Blog.

Start building on the Asia Pacific (Taipei) Region now.

–Betty

Broadcom Tomahawk 6 102.4T 64-port 1.6TbE Switches at Computex 2025

Post Syndicated from Rohit Kumar original https://www.servethehome.com/broadcom-tomahawk-6-102-4t-64-port-1-6tbe-switches-at-computex-2025-wiwynn-wistron-delta/

We spotted Broadcom Tomahawk 6 102.4T switches from several vendors at Computex 2025 in 64-port 1.6TbE configurations

The post Broadcom Tomahawk 6 102.4T 64-port 1.6TbE Switches at Computex 2025 appeared first on ServeTheHome.

[$] Zero-copy for FUSE

Post Syndicated from jake original https://lwn.net/Articles/1023689/

In a combined storage and filesystem session at the 2025 Linux Storage,
Filesystem, Memory Management, and BPF Summit (LSFMM+BPF), Keith Busch led
a discussion about zero-copy operations for the Filesystem
in Userspace
(FUSE) subsystem. The session was proposed
by his colleague, David Wei, who could not make it to the summit, so Busch
filled in, though he noted that “I do not really know FUSE so
well
“. The idea is to eliminate data copies in the data path to and
from the FUSE server in user space.

Use AI agents and the Model Context Protocol with Amazon SES

Post Syndicated from Zip Zieper original https://aws.amazon.com/blogs/messaging-and-targeting/use-ai-agents-and-the-model-context-protocol-with-amazon-ses/

Amazon Simple Email Service (Amazon SES) delivers a cloud-based email solution that empowers businesses to send emails more efficiently and at a larger scale. Its powerful, scalable platform enables organizations from startups to global brands to send personalized, high-volume email communications while maintaining exceptional deliverability and performance.

Amazon SES caters to a wide range of users, from developers and technical marketing professionals to business communicators. In addition to offering robust programmatic access through APIs and SMTP protocols, Amazon SES provides a comprehensive web console and intuitive dashboards that make email configuration and performance monitoring accessible to users with varying technical backgrounds. Historically, navigating email workflows and configuring advanced email capabilities in Amazon SES has required specialized knowledge, resulting in a learning curve for new users. As seen in many other areas, today’s AI tools can offer more intuitive ways to manage Amazon SES to get the most out of your email communications. We have found, however, that these AI tools occasionally produce inconsistent results, often as a result of the underlying large language model’s (LLM’s) training data.

Recognizing the need for a specialized, service-aware, AI-friendly Amazon SES solution, we are introducing the SESv2 MCP Server, a sample Model Context Protocol (MCP) for Amazon SES. We’ve integrated the SESv2 MCP Server sample with the Amazon SES v2 APIs to provide more precise and reliable AI-assisted use, management, and configuration for Amazon SES.

MCP is an open protocol that enables seamless integration between your AI-powered integrated development environment (IDE) or AI assistant, enriching the capabilities of the AI and enabling you to use Amazon SES using natural language. For more info, see the GitHub repo.

We’ve released the SESv2 MCP Server sample on GitHub and invite current and prospective customers to experiment with it in non-production environments. You can use it with your AI tools to explore ways in which AI can be used with Amazon SES to send emails, check configurations, and review deliverability. We’re interested in learning how you use your AI tools and the SESv2 MCP Server to test out email sending in different services or applications. We’re also curious if new customers find it helpful when configuring and learning about their Amazon SES service. No matter how you use it, we are eager for your feedback, comments, and contributions through the GitHub project’s issues.

Solution overview

You can use the SESv2 MCP Server sample with AI assistant applications like Anthropic’s Claude Desktop. You can also integrate it into MCP-compatible agentic AI coding assistants such as Amazon Q Developer, Amazon Q for command line, Cline, Cursor, and Windsurf. When used as an AI coding assistant, the SESv2 MCP Server sample helps developers add Amazon SES email capabilities to their applications and services using plain, natural language prompting. For recommendations from AWS on how to improve your vibe coding experience, refer to Vibe coding tips and tricks.

After you’ve configured the sample and authenticated with your AWS credentials, you can use natural language in your chosen AI tool. For example, an email marketing manager might want to ask Anthropic’s Claude Desktop “provide me with the status of the verified identities in my SES account, along with any recommendations to improve deliverability.” Someone new to Amazon SES can ask the Amazon Q CLI “create a new Amazon SES configuration set for the octank.com identity, enable it for event publishing for bounces and complaints.” Similarly, the developer of an AI-enabled restaurant booking application might ask the Amazon Q CLI “my application needs to send email confirmation of a customers online booking. Can you walk me thru adding this capability to my app using my SES account?”

As you can see from these examples, although it’s helpful to know a bit about email, and Amazon SES in general, with the help of your AI tool and the SESv2 MCP Server sample, you don’t need to be an email or Amazon SES expert. The combination of your creativity, AI tool, and the SESv2 MCP Server sample empowers even non-developers to create, test, and monitor Amazon SES workflows using natural language.

The SESv2 MCP Server sample release uses the open source Smithy Java project, which is still in development. As such, the SESv2 MCP Server is considered a sample, and we do not recommend employing it for production use. When a stable version is available, we might update this post and the GitHub repository accordingly.

Prerequisites

To follow along with the example use cases, make sure you have the following prerequisites set up:

  • AWS credentials with appropriate permissions.
  • An MCP-compatible LLM client (such as Anthropic’s Claude Desktop, Cline, Amazon Q CLI, or Cursor). For this post, we use the Amazon Q Developer CLI. For installation instructions, refer to Installing Amazon Q for command line.
  • Java 21 (or later) runtime (as required by Smithy Java).
  • Access to GitHub.
  • Git installed locally. For instructions, see Getting Started – Installing Git.

Best practices for using MCPs

To maximize the benefits of MCP-assisted development while maintaining security and code quality, we suggest you follow these essential guidelines:

  • Always review generated code for security implications before deployment
  • Use MCP servers as accelerators, not replacements for developer judgment and expertise
  • Keep MCP servers updated with the latest AWS security best practices
  • Follow the principle of least privilege when configuring AWS credentials
  • Run security scanning tools on generated infrastructure code

Configure the AWS CLI

Use the following command to configure the AWS Command Line Interface (AWS CLI) with the AWS credentials for your Amazon SES account and AWS Region:

aws configure

Clone and build the GitHub repository locally

To use macOS or Linux, use the following command to clone and build the GitHub repo:

git clone https://github.com/aws-samples/sample-for-amazon-ses-mcp.git
cd sample-for-amazon-ses-mcp
./build.sh

For Windows, use the following command:

git clone https://github.com/aws-samples/sample-for-amazon-ses-mcp.git
cd sample-for-amazon-ses-mcp
.\build.bat

Copy the absolute path to the .jar file (JAR_PATH_FROM_BUILD_OUTPUT). This will be printed at the end of the build script:

/<your path>/sample-for-amazon-ses-mcp/artifacts/sample-for-amazon-ses-mcp-all.jar

Configure your AI tool to use SESv2 MCP Server

When the build is complete, add SESv2 MCP Server to your AI tool’s MCP configuration:

{
  "mcpServers": {
    "sesv2-mcp-server": {
      "command": "java",
      "args": [
        "-jar",
        "JAR_PATH_FROM_BUILD_OUTPUT"
      ]
    }
  }
}

See MCP configuration for configuration steps. See the Claude Desktop MCP configuration guide for setup instructions.

After you build the SESv2 MCP Server and configure your AWS credentials, you’re ready to interact with Amazon SES. Keep in mind that effective, thoughtful prompting is crucial for successful AI-assisted development. For more information about vibe coding, see Vibe coding tips and tricks.

Example use cases

In this section, we provide some guided examples using the Amazon Q Developer CLI to interact with Amazon SES. Feel free to experiment on your own use cases, and share your comments and ideas through the GitHub project’s issues. Do not disclose any personal, commercially sensitive, or confidential information.

Get information, recommendations, and configurations your Amazon SES account

Open your AI tool; for these examples, we use a macOS terminal and initiate a chat session with the Amazon Q CLI:

q chat

We’ve found it useful to provide your AI tool with some guidance:

You're connected to the SESv2 MCP Server and have access to the AWS SESv2 APIs.

Ask the Amazon Q CLI about your AWS account’s SES email identities:

Tell me about the identities in my account, and also if the account is in the SES sandbox?

The Amazon Q CLI will request permission to use the SESv2 MCP Server (which provides the Amazon Q CLI with the SESv2 APIs ListEmailIdentities and GetAccount) to query your AWS SES account and reply with a detailed summary.

Ask the Amazon Q CLI if it has any recommendations related to improving deliverability for your Amazon SES account:

Do you have any recommendations to improve email deliverability for my SES account?

The Amazon Q CLI will use the SESv2 MCP Server (which provides the CLI with the SESv2 API ListRecommendations) to query your Amazon SES account and reply with a detailed summary.

Ask the Amazon Q CLI to set up Amazon SES click tracking for one of your domains. We have found it helpful to remind the CLI that it has access to additional knowledge of the AWS service APIs. It’s also a good idea to make sure the AI tool doesn’t invent nonexistent APIs.

You also have access to other AWS service APIs via the AWS CLI and your general knowledge, but you may only use known, documented APIs - do not invent or create any APIs or commands.
Set up Amazon SES click tracking with CloudWatch integration for the domain <my verified identity> to monitor email metrics. Use Amazon's default tracking domain (no SSL or https) for the click tracking to ensure immediate functionality without requiring custom domain setup. Include all necessary configuration steps and verify the setup works correctly. Create a test HTML email to <my email address> from <no-reply@verified domain> with subject "Testing SES click tracking". Create an HTML (with fallback to text) body with links and short descriptions taken from the public AWS webpages for Amazon SES, AWS End User Messaging and Amazon Connect. 

Send emails with your Amazon SES account

Using its knowledge of Amazon SES from the SESv2 MCP Server and permissions to use your Amazon SES account (aws configure), you can use your AI tool to create and send emails using Amazon SES.

If your Amazon SES account is in the Amazon SES sandbox, you are limited to sending and receiving email from verified email addresses. You are also limited to 200 messages in 24 hours. For more information about the Amazon SES sandbox, see Request production access (Moving out of the Amazon SES sandbox). If you’re in the sandbox, you can simply ask your AI tool “verify my email address <[email protected]>.”

Ask the Amazon Q CLI to send a test email with a sample HTML body:

Send a test email to <my verified email address> from <verified SES email identity>. Set the from email display name to "MCP testing". Make the email subject "Test sending an email via SES MCP". Use the information found on the Amazon SES website to create an HTML message body with a few sentences and bullet points about SES. Provide a text version of the message body in case of fallback.

Check your email, where you will receive a response.

You can get creative and ask the Amazon Q CLI to create a formatted email template with personalization using a simple table with email recipients, the product they bought, and their postal code:

Use the table below to send each person in the table an html formatted (with fallback) email message. 
-- table --
email,name,product,zipcode
<my verified email address>,Alice,an umbrella,98101
<my verified email address>,Bob,lots of sunscreen,10001
-- end table --
Use the template below. Create a 5-day weather forecast graphic similar to popular weather app graphics based on estimated weather for their ZIP code.
-- template --
"Hi {{name}}, thanks for buying {{product}}; it looks like you'll need it soon based on the 5-day weather forecast for your local area: <5-day weather forecast graphic>.

As we’ve demonstrated, you don’t need to be a seasoned developer to create and test Amazon SES workflows when you have an AI tool and the SESv2 MCP Server sample.

Conclusion

The SESv2 MCP Server sample democratizes the ability to configure, manage, and create sophisticated email automation workflows with Amazon SES.

The examples and guidance in this post demonstrate how even newcomers can use AI tools like the Amazon Q CLI to test out configuring, monitoring, and sending emails with Amazon SES using natural language. More technical users, including developers, can use the SESv2 MCP Server sample to build and test intelligent email applications that use Amazon SES, or to test out building Amazon SES sending into their own application.

We hope you will experiment with the SESv2 MCP Server sample and provide us with your thoughts and feedback, and perhaps contribute to the project through the GitHub project’s issues.

Additional resources

Introducing AWS API models and publicly available resources for AWS API definitions

Post Syndicated from Channy Yun (윤석찬) original https://aws.amazon.com/blogs/aws/introducing-aws-api-models-and-publicly-available-resources-for-aws-api-definitions/

Today, we’re announcing a new publicly available source of API models for Amazon Web Services (AWS). We are now publishing AWS API models on a daily basis to Maven Central and providing open source access to a new repository on GitHub. This repository includes a definitive, up-to-date source of Smithy API models that define AWS public interface definitions and behaviors.

These Smithy models can be used to better understand AWS services and build developer tools like custom software development kits (SDK) and command line interfaces (CLIs) for connecting to AWS or testing tools for validating your application integrations on AWS.

Since 2018, we have been generating SDK clients and CLI tools using Smithy models. All AWS services are modeled in Smithy to thoroughly document the API contract including operations and behaviors like protocols, authentication, request and response types, and errors.

With this public resource, you can build and test your own applications that can integrate directly with AWS services with confidence such as:

  • Generate SDK clients – You can build your own, purpose-built SDKs for language communities without official AWS SDK support and client code generator using Smithy toolchain to generate client SDK libraries.
  • Generating API implementations – You can generate server stubs for language-specific framework, even model context protocol (MCP) server configurations for your AI agents. You have built-in validation to ensure you adhere to your own API standards.
  • Build your own developer tools – You can build your own tools on top of AWS such as mock testing tools, IAM policy generators, or higher-level abstractions for connecting to AWS.
  • Understand AWS API behaviors – You can concisely and easily investigate your artifact to quickly review and understand how SDKs interpret API calls and the behaviors to expect with those calls.

Learn about AWS API models
You can browse the AWS service models directly on GitHub by accessing the api-models-aws repository. This repository contains Smithy models with the JSON AST format for all public AWS API services. All Smithy models consist of shapes and traits. Shapes are instances of types and traits are used to add more information to shapes that might be useful for clients, servers, or documentation.

The AWS models repository contains:

  • Top-level service directories are named using the <sdk-id> of the service, where <sdk-id> is the value of the model’s sdkId, lowercased and with spaces converted to hyphens
  • Each service directory contains one directory per <version> of the service, where <version> is the value of the service shape’s version property.
  • Contained within a service-version directory, a model file named <sdk-id>-<version>.json will be present

For example, when you want to define a RunInstances API in Amazon EC2 service, the model uses service type, an entry point of an API that aggregates resources and operations together. The shape referenced by a member is called its target.

com.amazonaws.ec2#AmazonEC2": {
      "type": "service",
      "version": "2016-11-15",
      "operations": [
....
        {
          "target": "com.amazonaws.ec2#RunInstances"
        },
....
	  ]

The operation type represents the input, output, traits, and possible errors of an API operation. Operation shapes are bound to resource shapes and service shapes. An operation is defined in the IDL using an operation_statement. In the traits, you can find detailed API information such as documentation, examples, and so on.

"com.amazonaws.ec2#RunInstances": {
      "type": "operation",
      "input": {
        "target": "com.amazonaws.ec2#RunInstancesRequest"
      },
      "output": {
        "target": "com.amazonaws.ec2#Reservation"
      },
      "traits": {
        "smithy.api#documentation": "<p>Launches the specified number of instances using an AMI for which you have....",
        smithy.api#examples": [
          {
            "title": "To launch an instance",
            "documentation": "This example launches an instance using the specified AMI, instance type, security group, subnet, block device mapping, and tags.",
            "input": {
              "BlockDeviceMappings": [
                {
                  "DeviceName": "/dev/sdh",
                  "Ebs": {
                    "VolumeSize": 100
                  }
                }
              ],
              "ImageId": "ami-abc12345",
              "InstanceType": "t2.micro",
              "KeyName": "my-key-pair",
              "MaxCount": 1,
              "MinCount": 1,
              "SecurityGroupIds": [
                "sg-1a2b3c4d"
              ],
              "SubnetId": "subnet-6e7f829e",
              "TagSpecifications": [
                {
                  "ResourceType": "instance",
                  "Tags": [
                    {
                      "Key": "Purpose",
                      "Value": "test"
                    }
                  ]
                }
              ]
            },
            "output": {}
          }
        ]
      }
    },

We use Smithy extensively to model our service APIs and provide the daily releases of the AWS SDKs and AWS CLI. AWS API models can be helpful for implementing server stubs to interact with AWS services.

How to build with AWS API models
Smithy API models provide building resources such as build tools, client or server code generators, IDE support, and implementations. For example, with Smithy CLI, you can easily build your models, run ad-hoc validation, compare models for differences, query models, and more. The Smithy CLI makes it easy to get started working with Smithy without setting up Java or using the Smithy Gradle Plugins.

I want to show two examples how to build your own applications with AWS API models and Smithy build tools.

  • Build a minimal SDK client – This sample project provides a template to get started using Smithy TypeScript to create a minimal AWS SDK client for Amazon DynamoDB. You can build the minimal SDK from the Smithy model, and then run the example code. To learn more, visit the example project here.
  • Build MCP servers – This sample project provides a template to generate a fat jar which contains all the dependencies required to run a MCP StdIO server using the Smithy CLI. You can find MCPServerExample to build an MCP server by modeling tools as Smithy APIs and ProxyMCPExample to create a proxy MCP Server for any Smithy service. To learn more, visit the GitHub repository.

Now available
You can now access AWS API models on a daily basis providing open-source access on the AWS API models repository and service model packages available on Maven Central. You can import models and add dependencies using the maven package of their choice.

To learn more about the AWS preferred API modeling language, visit Smithy.io and its code generation guide. To learn more each AWS SDKs, visit Tools to Build on AWS and its respective repository for SDK specific support or through your usual AWS Support contacts.

— Channy

Many voices, one community: Three themes from RSA Conference 2025

Post Syndicated from Anne Grahn original https://aws.amazon.com/blogs/security/many-voices-one-community-three-themes-from-rsa-conference-2025/

RSA Conference (RSAC) 2025 drew 730 speakers, 650 exhibitors, and 44,000 attendees from across the globe to the Moscone Center in San Francisco, California from April 28 through May 1.

The keynote lineup was eclectic, with 37 presentations featuring speakers ranging from NBA Hall of Famer Earvin “Magic” Johnson to public and private-sector luminaries such as former US National Cyber Director Chris Inglis, U.S. Secretary of Homeland Security Kristi Noem, and cryptography experts Tal Rabin, Whitfield Diffie, and Adi Shamir.

Topics aligned with this year’s conference theme, “Many Voices. One Community,” and focused on the security industry’s shared drive to foresee risks, counter threats, and embrace new challenges.

Three themes caught our attention: agentic AI, cryptography, and public-private collaboration.

Agentic AI

The potential of agentic AI to augment human decision-making was a common thread among conversations at the conference. Numerous sessions touched on the topic, and the desire of attendees to understand the technology and learn how to balance its risks and opportunities was clear.

Separating hype from reality

An AI agent is a software program that can interact with its environment (as detailed in Figure 1), collect data, and use the data to perform self-determined tasks to meet predetermined goals.

Figure 1: Generative AI agents

Figure 1: Generative AI agents

Agentic systems offer a fundamentally different approach compared to traditional software, particularly in their ability to handle complex, dynamic, and domain-specific challenges. While traditional systems rely on rule-based automation and structured data, agentic systems use large language models (LLMs)—a subset of generative AI—to operate autonomously. Agents can learn from interactions with users, and make nuanced, context-aware decisions while keeping human analysts in the loop.

Numerous RSAC speakers alluded to AI agents as the next frontier in enterprise transformation. Gartner® predicts that: “By 2028, 33% of enterprise software applications will include agentic AI, up from less than 1% in 2024,” and “at least 15% of day-to-day work decisions will be made autonomously through agentic AI, up from zero percent in 2024.”

However, as organizations build AI agents, understanding the concerns that come with them is critical.

“Agentic AI presents tremendous opportunities to deliver business value and innovative security outcomes. Production deployments require a balance between its capabilities, and robust security and trust mechanisms.”
—Hart Rossman, Global Services Security Vice President at AWS

In the RSAC keynote session The Five Most Dangerous New Attack Techniques…and What to Do for Each, Rob Lee, Chief of Research and Head of Faculty at SANS Institute noted that while security teams are embracing AI to amplify productivity, threat actors are doing the same. He pointed to MIT research that shows adversarial agent systems executing attack sequences are 47 times faster than human operators, with a 93 percent success rate in privilege escalation paths.

Safeguarding GenAI & Agentic Apps, Top 10 Risks in 2025, a half-day Open Worldwide Application Security Project (OWASP) event, focused on helping attendees distinguish real threats from hype. OWASP Gen AI Security Project team members and industry experts reviewed the 2025 OWASP Top 10 List for LLM and GenAI (shown in Figure 2), and introduced Agentic AI—Threats and Mitigations—the first in a series of guides from the OWASP Agentic Security Initiative (ASI) to provide a threat-model-based reference of emerging agentic threats and mitigations. Content feedback can be submitted to ASI in advance of the guide’s next release.

Figure 2: 2025 OWASP Top 10 for LLM Applications

Figure 2: 2025 OWASP Top 10 for LLM Applications

Agentic AI wins Cybersecurity Startup Accelerator

The second annual AWS and CrowdStrike Cybersecurity Startup Accelerator, in collaboration with the NVIDIA Inception program, took place during RSAC. A panel of judges—including George Kurtz, Founder and CEO of CrowdStrike, CJ Moses, Chief Information Security Officer at Amazon, and David Reber Jr., Chief Security Officer at NVIDIA—evaluated startups on innovation, market relevance, and go-to-market potential. Terra Security, a provider of agentic AI-powered, continuous web application penetration testing, was selected from a group of 10 finalists who pitched live. Two runners-up, Kenzo Security and Rig Security, were also recognized for their standout approaches to agentic AI-driven security.

Addressing AI risks

The need to consider your security posture when assessing overall AI readiness was emphasized throughout the conference. A defense-in-depth architecture can help mitigate risks with multiple layers of protection across both traditional and AI software components. Innovative solutions such as AI red teaming, AI behavioral sandboxing, and advanced tracing and evaluation of generative AI agents can enhance your security strategy with a proactive approach to securing AI.

Visit the following resources to help design, build, and operate AI systems: DevsecOps Revolution: Unleashing Generative AI for Automated Excellence, AWS generative AI security, responsible AI, and the Amazon AGI Labs Blog.

Cryptography

Encryption was another key topic. The FIDO Alliance hosted a half-day seminar that focused on developments in the global movement to passwordless technology such as passkeys—cryptographic keys designed to replace passwords by combining the power of public key cryptography with biometric authentication.

In Dude, Where’s My Password? The Challenges of Getting to Passwordless, Andy Ozment, Chief Technology Risk Officer and Executive Vice President at Capital One noted that 88 percent of data compromised in basic web application attacks reported in 2024 involved stolen credentials. Ozment pointed out that “going passwordless” through a combination of X.509 device certificates and FIDO2 passkeys presented Capital One with an opportunity to nearly eliminate entire classes of threats (as detailed in Figure 3), while increasing the quality of user experience.

Figure 3: Using passkeys to reduce risk while advancing user experience

Figure 3: Using passkeys to reduce risk while advancing user experience

Along the way, Ozment said, Capital One’s journey to passwordless was enabled by its transition from on-premises technology to going “all-in” on the public cloud. Watch the recording of his session or view the slides to learn more.

Post-quantum encryption

The state of post-quantum encryption was detailed in the popular Cryptographer’s Panel, moderated by Tal Rabin, Senior Principal Applied Scientist at AWS.

Panelist Vinod Vaikuntanathan, Professor at MIT underscored the impact of the quantum-resistant algorithm standardization process (Figure 4) started by the National Institute of Standards and Technology (NIST) in 2016. “We now have two public key encryption algorithms, and three new digital signature algorithms that are standardized,” he pointed out.

Figure 4: Post-quantum encryption algorithms

Figure 4: Post-quantum encryption algorithms

The panelists agreed that even though quantum computers aren’t here yet, the time to deploy these algorithms is now. NIST recommends phasing out existing encryption methods by 2030 in its Transition to Post-Quantum Cryptography Standards report. However, Vaikuntanathan and Adi Shamir, the “s” in the Rivest–Shamir–Adleman (RSA) public-key cryptosystem, advise organizations to take a hybrid approach that combines classic encryption algorithms such as RSA or Elliptic-curve Diffie–Hellman (ECDH) with post-quantum algorithms such as Module-Lattice-based Key Encapsulation Mechanism (ML-KEM). This approach, which is used by AWS and recommended by The European Commission, offers protection against both current and future threats.

RSAC Award for Excellence in the Field of Mathematics

Dr. Shai Halevi, Senior Principal Applied Scientist at AWS, was presented with the Award for Excellence in the Field of Mathematics for remarkable contributions to many areas of cryptography, including fundamental theory, advanced cryptographic primitives, secure multi-party computations, homomorphic encryption, and cryptographic code obfuscation.

Figure 5: Dr. Shai Halevi receives RSAC award for Excellence in the Field of Mathematics

Figure 5: Dr. Shai Halevi receives RSAC Award for Excellence in the Field of Mathematics

End-to-end encryption

Concerns about the recent US government group chat leak were also raised during the discussion. Public-key cryptography pioneer Whitfield Diffie noted that the use of an encrypted consumer messaging app to communicate classified information broke archiving laws. Because some commercial tools use 256-bit Advanced Encryption Standard (AES) encryption, which is “good enough” to protect communications, he predicted an increase in the use of consumer applications to protect sensitive information in unapproved ways.

The Cybersecurity and Infrastructure Security Agency (CISA) and the Federal Bureau of Investigation (FBI) recently advised individuals and organizations to start using encrypted messaging apps. However, as the role of these applications in business communication expands, it’s important not to lose sight of recordkeeping and compliance obligations. Organizations should consider solutions that offer administrative controls and data retention capabilities along with encryption.

AWS Wickr, for example, is a messaging and collaboration service that protects messaging, calling, file sharing, screen sharing, and location sharing with 256-bit end-to-end encryption. The data retention and administrative controls that it provides help customers meet regulatory requirements and manage user and device data remotely.

Wickr is Department of Defense Cloud Computing Security Requirements Guide Impact Level 5 (DoD CC SRG IL5) and Federal Risk and Authorization Management Program (FedRAMP) High authorized in the AWS GovCloud (US-West) Region. It also meets compliance programs and standards such as Health Insurance Portability and Accountability Act (HIPAA) eligibility, International Organization for Standardization (ISO) 27001, and System and Organization Controls (SOC) 1, 2, and 3.

Visit the AWS News Blog and the AWS Security Blog to learn about AWS passkey multi-factor authentication, how AWS is migrating to post quantum cryptography (PQC), and how we can help you implement a layered encryption strategy for your organization.

Public-private collaboration

Numerous sessions underlined the importance of collaboration to strengthening security. In his keynote, Johnson called attention to a lesson he learned on the basketball court—his peers made him stronger. “Larry Bird made me a better basketball player,” he said, relating his experience to the need for security teams to assist and learn from each other.

In Making America Safe Again Through Cyber Defense, Kristi Noem, U.S. Secretary of Homeland Security equated cybersecurity with national security, and insisted that building on public-private partnerships is “incredibly important.” “Our goal,” she said, “is to use our maximum effect of cooperation to make sure that we’re going after bad actors.”

After assuring attendees that CISA will continue to be America’s cyber defense agency, she urged congress to reauthorize the Cybersecurity Information Sharing Act of 2015. The law, which is set to expire in September, incentivizes businesses to share threat indicators with the Department of Homeland Security (DHS) and helps make sure that both the federal government and companies can take collaborative steps to address threats.

Panelists at an offsite threat intelligence discussion reiterated the ability of private industry to supplement government security capabilities. Adam Meyers, Senior VP, Counter Adversary Operations at CrowdStrike pointed out that technology companies often have more data and signals than governments. The CrowdStrike Falcon solution, he said, processes over 6 trillion events per day, and 55 million events per second at peak. This volume facilitates the detection of threat patterns that might otherwise go unnoticed.

Similarly, Moses noted that the size and scale of AWS infrastructure gives us unique visibility into internet traffic. Our global network of sensors and associated disruption tools observe over 700 million threat interactions every day, out of which 450 million can be classified as malicious. Internal threat intelligence tools such as MadPot, our sophisticated global honeypot system, produce high-fidelity findings (pieces of relevant information) that can be used to drive proactive intelligence sharing, and reduce investigative workloads.

“We’ll work together in order to be able to put a bow on a case and hand it to the FBI and DOJ, such that they don’t have to expend a great amount of resources in order to go forward and try to figure things out that we already know.” —CJ Moses, Chief Information Security Officer and VP of Security Engineering at Amazon

An example of this is the disruption of the cybercriminal group known as Anonymous Sudan. The group was responsible for tens of thousands of distributed denial-of-service (DDoS) attacks against critical infrastructure, corporate networks, and government agencies. With the help of tools like MadPot, AWS experts were able to identify the hosting provider infrastructure that the group used to launch the DDos attacks, and work with providers to disrupt them. Akamai SIRT, Cloudflare, CrowdStrike, DigitalOcean, Flashpoint, Google, Microsoft, PayPal, SpyCloud, and other private sector entities also assisted law enforcement, leading to the indictment of two Anonymous Sudan leaders.

The value of combined perspectives

RSA Conference 2025 might be over, but the learning continues. Additional highlights that include the west stage keynotes, the Innovation Sandbox, and dozens of insightful sessions on topics such as the changing role of the CISO, women in cyber, and of course—cloud security—are available on demand.

If there’s one key takeaway, it’s a collective sense of transition. As we explore the benefits and risks of emerging AI technologies, encryption strategies, and information sharing, it’s important to remember that we cannot effectively combat threats in isolation. Security is a collective endeavor; only by working together can we adapt to evolving challenges and build cyber resilience.

For more information about cloud security, register to join AWS, Google Cloud, and Microsoft online at the SANS 2025 Cloud Security Exchange on August 21.

Anne Grahn

Anne Grahn

Anne is a Senior Worldwide Security GTM Specialist at AWS, based in Chicago. She has 15 years of experience in the security industry and focuses on effectively communicating cybersecurity risk. She maintains a Certified Information Systems Security Professional (CISSP) certification.

Streamline your Eclipse workflows with Amazon Q Developer, now generally available

Post Syndicated from Madhu Balaji original https://aws.amazon.com/blogs/devops/streamline-your-eclipse-workflows-with-amazon-q-developer-now-generally-available/

Today, we’re excited to announce the general availability of Amazon Q Developer plugin for the Eclipse integrated development environments (IDE). This release builds upon the developer experience introduced in our November 2024 public preview, bringing powerful AI-assisted development capabilities directly into Eclipse 2025-03(4.35.0) and later versions. The integration significantly improves how developers write, test, and maintain code by providing intelligent code suggestions, automated code generation, and real-time AI assistance within their familiar IDE environment.

Understanding the agentic coding experience

At its core, Amazon Q Developer functions as an intelligent coding companion in your Eclipse IDE, offering real-time collaboration through natural language interaction. What sets it apart is its agentic nature – Amazon Q Developer understands your project structure, can read and modify files, execute commands, and maintain conversation history throughout your development session. This deep integration helps developers stay focused within their IDE while leveraging AI assistance for various development tasks.

As a developer working on complex projects, I’m particularly excited to see Amazon Q Developer’s agentic coding experience now available in Eclipse IDE. It’s not just a passive tool – it’s an active participant that provides transparent reasoning for its suggestions and gives developers choice between automated modifications or step-by-step confirmation of changes. Amazon Q Developer maintains awareness of your entire conversation history and project workspace, making each interaction more meaningful and productive. This deep contextual understanding allows developers to receive accurate and targeted assistance, bringing the same powerful development experience that has already transformed how developers work in other IDEs.

Key Capabilities and Features

Amazon Q Developer brings a comprehensive set of capabilities designed to enhance your development workflow in Eclipse IDE:

Interactive development support: Through natural language interactions, Amazon Q Developer assists with code generation, bug fixing, tests and optimization. You can describe your requirements conversationally, and the Amazon Q Developer will suggest implementations while explaining its reasoning. This includes generating entire functions, classes, or application components while maintaining consistency with your existing codebase.

Context actions: Using special prompts like @workspace, @files, and @folders, Amazon Q Developer can access and understand specific parts of your project. For example, @workspace provides full visibility of your project structure, while @files lets you focus on specific files for targeted assistance. This granular control ensures that Amazon Q Developer’s responses are precisely tailored to the relevant parts of your codebase.

Rules and standards configuration: Teams can establish custom development standards by configuring rules in the .amazonq/rules/ directory. These rules govern coding standards, testing requirements, security protocols, and documentation practices. For example, you can define specific patterns for error handling, logging standards, or architectural preferences that Amazon Q Developer will follow in its suggestions and code generation.

Multi-language Support: Amazon Q Developer supports interactions in multiple languages, including English, Mandarin, French, German, Italian, Japanese, Spanish, Korean, Hindi, and Portuguese. This allows developers to communicate with Amazon Q Developer in their preferred language while maintaining the same level of development support.

Let’s see it in Action

To begin using Amazon Q Developer for the first time, follow the steps in the Getting Started with Amazon Q Developer guide to access Amazon Q Developer. When using Amazon Q Developer, you can choose between Amazon Q Developer Pro, a paid subscription service, or Amazon Q Developer Free tier with AWS Builder ID user authentication.

For existing users, update to the new version. Refer to Using Amazon Q Developer in the IDE for activation instructions.

To start, you select the Amazon Q Developer icon in the IDE to open the chat interface. By default, agentic chat is turned on. You can turn off the agentic chat by toggling the button in the chat.

Eclipse IDE interface showing Amazon Q Developer chat window with welcome message and file navigation panel on the left side

Amazon Q Developer’s welcome interface within Eclipse IDE

Start by describing your requirement in plain language

I started by asking Amazon Q Developer to help me create a REST API endpoint for user registration.

Help me create a REST API endpoint for user registration in the @workspace

After analyzing my workspace, Amazon Q Developer outlined a comprehensive plan that included creating a User model, registration controller, and setting up project dependencies. Noticing my project needed a proper build configuration, Amazon Q Developer proposed creating a Maven-based Spring Boot application structure and provided the necessary directory setup commands – demonstrating how Amazon Q Developer guides developers through the development process step by step.

Amazon Q Developer conversation interface showing step-by-step guidance for creating a REST API endpoint, including project structure analysis and Maven configuration setup

Step-by-step project setup guidance from Amazon Q Developer

Amazon Q Developer provides a structured solution with explanation

Following Amazon Q Developer’s guidance, I quickly had a fully functional REST API endpoint for user registration. Amazon Q Developer provided a comprehensive implementation, including a proper Maven project structure, essential model classes with validation, a REST controller, and the main application class. Amazon Q Developer even outlined the API usage, showing the expected JSON request format and response structure. It’s impressive how Amazon Q Developer not only generated the code but also included practical notes on validation and suggestions for production-ready improvements, demonstrating its understanding of best practices in software development.

Detailed summary screen showing the complete implementation of a REST API endpoint, including project structure, model classes, controller configuration, and JSON request/response examples

Complete REST API implementation summary with code examples

Build and run the application

With Amazon Q Developer’s guidance, I progressed from project setup to a running application. Amazon Q Developer helped me build the project successfully, and I was able to run the Spring Boot application, watching as it initialized and started up. The console output confirmed that Tomcat was running and my UserApiApplication had launched successfully, demonstrating how Amazon Q Developer streamlines the development process from code generation to a functioning API endpoint.

Terminal output showing successful Spring Boot application build and succesful startup with Maven build logs

Amazon Q Develeper agentic coding builds the application

Console output showing successful Spring Boot application startup logs with Tomcat server initialization, displaying timestamps and INFO messages indicating the application started on port 8080 with a total startup time of 1.57 seconds.

Successful build and launch of the Spring Boot REST API application

Multi-language support in Eclipse IDE

Side-by-side comparison of Amazon Q Developer conversations in English, Spanish, French and Hindi, all discussing the creation of a REST API endpoint for user registration in SpringBoot.

Q Developer supports multiple languages

Sample rules and standard setup for a project

A sample rule file for Spring Boot applications, stored in the .amazonq/rules directory at the project root, guides Amazon Q Developer’s actions.

# Spring Boot Project Setup for Eclipse IDE

Rules for setting up a standard Java Spring Boot 3-tier web application backend in Eclipse IDE

## Project Structure

Standard Spring Boot 3-tier application structure:
- `src/main/java/${packagePath}/controller`: REST controllers
- `src/main/java/${packagePath}/service`: Business logic services
- `src/main/java/${packagePath}/repository`: Data access repositories
- `src/main/java/${packagePath}/model`: Domain models/entities
- `src/main/java/${packagePath}/dto`: Data Transfer Objects
- `src/main/java/${packagePath}/exception`: Custom exceptions
- `src/main/java/${packagePath}/config`: Configuration classes
- `src/main/resources`: Configuration files, static resources, templates
- `src/test/java`: Test source code
- `src/test/resources`: Test configuration and resources

## Eclipse Configuration

Eclipse-specific settings:
- Java Compiler: Java 17
- Project Facets: Java
- Maven Integration
- Spring Tools 4 support

## Maven Configuration

Standard Maven configuration for Spring Boot:
- groupId: `${groupId:com.example}`
- artifactId: `${artifactId:demo}`
- version: `${version:0.0.1-SNAPSHOT}`
- name: `${name:demo}`
- description: `${description:Spring Boot Demo Project}`

### Dependencies
- org.springframework.boot:spring-boot-starter-web
- org.springframework.boot:spring-boot-starter-data-jpa
- org.springframework.boot:spring-boot-starter-validation
- org.springframework.boot:spring-boot-starter-test
- org.springframework.boot:spring-boot-devtools
- com.h2database:h2

## Application Properties

Standard application properties configuration:
```properties
# Server configuration
server.port=${serverPort:8080}
spring.application.name=${applicationName:demo}

# Database configuration
spring.datasource.url=jdbc:h2:mem:testdb
spring.datasource.driverClassName=org.h2.Driver
spring.datasource.username=sa
spring.datasource.password=password
spring.jpa.database-platform=org.hibernate.dialect.H2Dialect
spring.h2.console.enabled=true

# Logging
logging.level.root=INFO
logging.level.org.springframework.web=INFO
logging.level.org.hibernate=ERROR
```

Amazon Q Developer analyzes the workspace and creates a complete Spring Boot REST API project structure, including the Maven POM file, application properties, and appropriate directory hierarchy. It follows defined standard rules to ensure the project setup aligns with best practices, saving developers time and reducing setup complexity.

Getting Started

To begin using Amazon Q Developer in Eclipse IDE:

  1. Install Eclipse IDE 2025-03 or later
  2. Configure AWS credentials in your environment
  3. Install Amazon Q Developer plugin from Eclipse Marketplace or go to Help > Eclipse Marketplace , search for Amazon Q > Install

Conclusion

With the addition of Amazon Q Developer in Eclipse IDE, developers now have access to AI-assisted development capabilities directly within their familiar development environment. The agentic coding experience brings an intelligent, interactive coding companion to Eclipse IDE users, enabling them to write, test, and maintain code more efficiently. Features like multi-language support , customizable rules for team standards, and powerful workspace commands make Amazon Q Developer a valuable addition to the Eclipse IDE ecosystem.

As we continue to enhance Amazon Q Developer’s agentic coding capabilities in Eclipse IDE, we remain committed to supporting developers in their daily development tasks. Amazon Q Developer actively participates in your development process, offering real-time suggestions, generating code, and adapting to your project’s specific needs. We invite you to explore Amazon Q Developer in Eclipse IDE and experience how this agentic AI can transform your development workflow.

To learn more about Amazon Q Developer’s features and pricing details, visit the Amazon Q Developer product page.


Madhu Balaji

Madhu is a Senior Specialist Solutions Architect at AWS who helps customers design and implement innovative cloud solutions. With 20+ years of experience in development and application architecture, he focuses on enabling customers to accelerate their time-to-market and solve complex business challenges using AWS services.

Introducing an agentic coding experience in Visual Studio and JetBrains IDEs

Post Syndicated from Artur Rodrigues original https://aws.amazon.com/blogs/devops/introducing-an-agentic-coding-experience-in-visual-studio-and-jetbrains-ides/

Developers spend countless hours on repetitive tasks like debugging code, writing unit tests, and validating build processes – time that could be better spent on innovation and problem-solving. To address these challenges, Amazon Q Developer has expanded its intelligent coding assistant capabilities to Visual Studio and JetBrains Integrated development environments (IDEs). This new agentic experience works proactively on your behalf, automatically analyzing your workspace, generating code fixes, and executing commands to streamline your development workflow.

In this blog post, we’ll explore how Amazon Q Developer automates unit test creation and execution to validate code changes, streamlines build processes by identifying and resolving common issues.

In May 2025, our colleague Brian Beach wrote about the new agentic coding experience in Amazon Q Developer for VS Code. By extending the agentic experience to Visual Studio and JetBrains IDEs, Amazon Q Developer now brings intelligent automation to even more developers.

Benefits for Developers

Amazon Q Developer transforms the way developers work by seamlessly integrating AI assistance into their daily workflow without switching contexts or leaving their preferred development environment. Using features like @workspace and @files, you can get highly relevant recommendations in your IDE. With Q Developer’s ability to take actions like generating code diffs and running commands, you can automate repetitive coding tasks, implement complex features faster, and troubleshoot issues without breaking your flow. With support for multiple languages including English, Mandarin, Japanese, and Spanish, Amazon Q Developer makes advanced AI assistance accessible to development teams worldwide, fostering inclusive collaboration across global organizations.

Maximizing Development Efficiency with Amazon Q Developer

Amazon Q Developer revolutionizes your development workflow by offering a comprehensive set of capabilities within your IDE. Let’s explore how this powerful tool leverages context to enhance your coding experience by using context features, codebase’s folders and rules.

You can explicitly guide Q Developer by defining specific files or folders in the prompt context. Don’t know where to find particular information? No problem! Q Developer can efficiently navigate through your codebase using @workspaces to gather relevant code snippets from multiple files. This is particularly important when you want to create documentation that spans multiple files or when you need to fix a bug and have no idea where you should start.

The agentic chat feature automatically derives context from the codebase’s folders and executes commands on your behalf. It has the same intelligent reasoning capability used in the Q Developer CLI, which has already won the hearts of many developers.

Context management extends to configuration through the .amazonq/rules/ directory. Within this directory, you can define rules for coding standards, testing requirements, security protocols, and documentation practices. Some customers have already created a rule that defines how Q Developer commits changes. This rule provides a template for a Git commit that details the message and for the agentic actions that modify files. It makes it much easier to identify and review the contributions of the Q Developer to your codebase.

Quick Tour of the Agentic Experience

Let us walk you through two use cases. In our example, we will use the Visual Studio IDE. Similar agentic capabilities are now supported in JetBrains IDEs as well. We invite you to follow along by cloning the Bob’s Used Books sample repo and opening it in Visual Studio 2022. Don’t forget to add or update the Amazon Q Developer extension.

Creating unit tests

The Bookstore.Domain project contains domain objects such as Book and ShoppingCart.

Bookstore.Domain project contains Book and Shopping cart classes.

Figure 1: Domain objects in Bookstore.Domain

We have a separate project called Bookstore.Domain.Tests that contains tests for the Book class.

A separate project - Bookstore.Domain.Tests contains tests for the Book class. BookTests class contains these tests.

Figure 2: Tests for Book class

We want to add unit tests for the ShoppingCart class. Let’s ask Amazon Q Developer to create unit tests for ShoppingCart. We also want Amazon Q Developer to follow the existing pattern of creating test classes in a separate test project.

By default, the agentic experience is on. If you are in the planning phase of the Software Development Lifecycle (SDLC) and prefer to use a traditional back-and-forth chat, you can turn the agentic experience. To toggle the agentic experience on and off, choose the angle bracket pair in the bottom left corner of your Q Developer chat window.

Then, we ask Q Developer “Can you create a test for @ShoppingCart.cs? Look at existing test and use the same libraries”. First, notice that we are giving a command instead of just asking a question. Second, we are referencing the file ShoppingCart.cs explicitly to provide Q Developer the appropriate context. In the following image, you can see that Q Developer is acting on our behalf. In agentic coding mode, Q Developer can take actions and run commands. In our example, it is reading files, writing to files, and running commands with your permission.

The agentic experience in Amazon Q Developer responding to our prompt and reading files in our workspace to gather context.

Figure 3: Prompt to create new tests

Using commands, Q Developer was able to analyze our solution structure, understand that we have a project called Bookstore.Domain.Tests, and create a new file containing unit tests for ShoppingCart.

The agentic experience in Amazon Q Developer generating a summary of the test cases it has created.

Figure 4: Summary of test cases

We can verify that there is a new file called ShoppingCartTests in the Bookstore.Domain.Tests project, which is aligned with our existing test creation strategy.

New file - ShoppingCartTests.cs contains the tests for ShoppingCart. Following the existing pattern in our code, Q Developer creates this file in the Bookstore.Domain.Tests project.

Figure 5: New file with generated test cases

In Visual Studio, we can now run the unit tests and verify that they pass.

Test results for the existing as well as new tests.

Figure 6: Successful test run of new tests

Resolving build errors

In the following example, we will demonstrate the power of the agentic coding experience by using Q Developer to build our application and resolve build errors.

In our example, we have deliberately misspelled one of the methods in the IShoppingCartRepository interface. The AddAsync method is now incorrectly spelled AddAsyn.

Spelling mistake in the name of a method. It is called AddAsyn instead of AddAsync.

Figure 7: Spelling mistake in a method name

When we try to build the Bookstore.Domain project, we get a build error as expected. Let’s ask Q Developer to fix the error. Without the agentic coding experience, we would have to copy the text of the build error into the chat window and ask Q Developer to provide recommendations. Then we would have to act on its recommendations by manually making changes and trying to build. This is one of many examples of the power of the agentic chat, which runs commands and uses the command’s output to enrich the context of the prompt to take actions.

With the agentic coding experience, we just ask Q Developer “Can you fix the error I am getting while building the solution? Please build and check it”. In the following image, you will see how Q Developer runs the .NET build commands to get build errors and read the relevant files.

Amazon Q Developer builds the solution, uses the build error to read the appropriate file, and finds the issue.

Figure 8: Building the solution

After it reads the files, it finds the spelling mistake and fixes it automatically. As shown in the following image, it then builds the solution to verify that its fix worked.

Amazon Q Developer fixes the spelling mistake in the code and runs the build again to confirm a successful build.

Figure 9: Fixing the spelling mistake

In the following image, Amazon Q Developer provides a summary of the error, the actions it took to build it. It even helps me with some recommendations to fix the warnings it got while running the build.

Amazon Q Developer provides a summary of build error, the resolution, and suggestions to resolve build warnings.

Figure 10: Summary of changes and suggestions

Conclusion

The addition of Amazon Q Developer’s agentic experience in Microsoft Visual Studio and JetBrains IDEs takes Amazon Q Developer beyond traditional chat-based interactions to intelligent, action-oriented assistance. The ability to automatically read files, generate code diffs, run shell commands, and validate changes demonstrates a level of autonomy that can significantly accelerate development tasks while maintaining code quality. The examples we’ve explored, from automated test creation to build error resolution, showcase how the agentic experience can streamline common development tasks that traditionally required multiple manual steps. This new capability, combined with multi-language support and customizable development standards, makes Amazon Q Developer a powerful ally in modern software development workflows. As development teams continue to seek ways to improve productivity without compromising code quality, Amazon Q Developer’s agentic experience represents a meaningful step forward in IDE-integrated AI assistance. Whether you’re writing tests, fixing bugs, or optimizing code, the ability to have an AI assistant that can not only suggest solutions but also implement them while maintaining context awareness is a game-changing addition to the developer’s toolkit.

Artur Rodrigues

Artur Rodrigues is a Principal Solutions Architect for Generative AI at Amazon Web Services (AWS), focused on the Next Generation Developer experience, enabling developers to work more efficiently and creatively through the integration of Generative AI into their workflows. Artur enjoys cycling and exploring the great outdoors of beautiful British Columbia in Canada. He is also a gelato aficionado and a fan of soccer and jiu-jitsu.

Neeraj Handa

Neeraj Handa is a Specialist Solutions Architect at Amazon Web Services, where he partners with enterprise customers to accelerate application development and modernization using Amazon Q Developer. He is passionate about helping organizations transform their software development lifecycle to achieve higher productivity and software quality through the use of AI technologies.

[$] Open source and the Cyber Resilience Act

Post Syndicated from daroc original https://lwn.net/Articles/1023306/

The European Union’s

Cyber Resilience Act
(CRA) has caused a stir in the
software-development world. Thanks to advocacy by the Eclipse Foundation, Open
Source Initiative, Linux Foundation, Mozilla, and others, open-source software
projects generally have minimal requirements under the CRA
— but nothing to do with law is ever quite
so simple. Marta Rybczyńska spoke at Linaro Connect 2025 about the impact of the
CRA on the open-source ecosystem, with an emphasis on the importance of
understanding a project’s role under the CRA. She later participated in a panel
discussion with Joakim Bech, Kate Stewart, and Mike Bursell about how the CRA
would impact embedded open-source development.

Announcing up to 45% price reduction for Amazon EC2 NVIDIA GPU-accelerated instances

Post Syndicated from Channy Yun (윤석찬) original https://aws.amazon.com/blogs/aws/announcing-up-to-45-price-reduction-for-amazon-ec2-nvidia-gpu-accelerated-instances/

Customers across industries are harnessing the power of generative AI on AWS to boost employee productivity, deliver exceptional customer experiences, and streamline business processes. However, the growth in demand for GPU capacity has outpaced industry-wide supply, making GPUs a scarce resource and increasing the cost of securing them.

As Amazon Web Services (AWS) grows, we work hard to lower our costs so that we can pass those savings back to our customers. Regular price reductions on AWS services have been a standard way for AWS to pass on the economic efficiencies gained from our scale back to our customers.

Today, we’re announcing up to 45 percent price reduction for Amazon Elastic Compute Cloud (Amazon EC2) NVIDIA GPU-accelerated instances: P4 (P4d and P4de) and P5 (P5 and P5en) instance types. This price reduction to On-Demand and Savings Plan pricing applies to all Regions where these instances are available. The pricing reduction applies to On-Demand purchases beginning June 1 and to Savings Plan purchases effective after June 4.

Here is a table of price reductions percentage (%) from May 31, 2025 baseline prices by instance types and pricing plans:

Instance type NVIDIA GPUs On-Demand EC2 Instance Savings Plans Compute Savings Plans
1 year 3 years 1 year 3 years
P4d A100 33% 31% 25% 31% –
P4de A100 33% 31% 25% 31% –
P5 H100 44% – 45% 44% 25%
P5en H200 25% – 26% 25% –

Savings Plans are a flexible pricing model that offer low prices on compute usage, in exchange for a commitment to a consistent amount of usage (measured in $/hour) for a 1- or 3- year term. We offers two types of Savings Plans:

  • EC2 Instance Savings Plans provide the lowest prices, offering savings in exchange for commitment to usage of individual instance families in a Region (for example, P5 usage in the US (N. Virginia) Region).
  • Compute Savings Plans provide the most flexibility and help to reduce your costs regardless of instance family, size, Availability Zones, and Regions (for example, from P4d to P5en instances, shift a workload between US Regions).

To provide increased accessibility to reduced pricing, we are making at-scale On-Demand capacity available for:

  • P4d instances in the Asia Pacific (Seoul), Asia Pacific (Sydney), Canada (Central), and Europe (London) Regions
  • P4de instances in the US East (N. Virginia) Region
  • P5 instances in the Asia Pacific (Mumbai), Asia Pacific (Tokyo), Asia Pacific (Jakarta), and South America (São Paulo) Regions
  • P5en instances in the Asia Pacific (Mumbai), Asia Pacific (Tokyo), and Asia Pacific (Jakarta) Regions

We are also now delivering Amazon EC2 P6-B200 instances through Savings Plan to support large scale deployments, which became available on May 15, 2025 at launch only through EC2 Capacity Blocks for ML. EC2 P6-B200 instances, powered by NVIDIA Blackwell GPUs, accelerate a broad range of GPU-enabled workloads but are especially well-suited for large-scale distributed AI training and inferencing.

These pricing updates reflect the AWS commitment to making advanced GPU computing more accessible while passing cost savings directly to customers.

Give Amazon EC2 NVIDIA GPU-accelerated instances a try in the Amazon EC2 console. To learn more about these pricing updates, visit Amazon EC2 Pricing page and send feedback to AWS re:Post for EC2 or through your usual AWS Support contacts.

— Channy

The collective thoughts of the interwebz