Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=uU9sPFHoPYE
Home Assistant 2026.11 Is Here — HACS Becomes Marketplace!
Post Syndicated from BeardedTinker original https://www.youtube.com/watch?v=VSs94oqUXOE
Bazzite 45 released
Post Syndicated from jzb original https://lwn.net/Articles/1105395/
Version
45 of Bazzite, the image-based gaming distribution based on
Fedora Linux, has been released. Notable changes in this release include a
rebase to Fedora 45, updated Open Gaming Collective (OGC)
kernels, support for Logitech TrueWheel devices, and more.
LWN covered Bazzite in
December 2025.
[$] Portable Python scripts with dependencies
Post Syndicated from jake original https://lwn.net/Articles/1104646/
A basic Python script is portable: it can be copied between machines with little concern about compatibility.
A script that depends on third-party packages requires quite a bit more
care and consideration, however.
In 2023, PEP
723 (“Inline script metadata”) introduced a standard for declaring a Python script’s
dependencies inside the script itself.
Several third-party tools can now automatically install and manage those dependencies, but there is still little official support for this standard within Python itself.
Security updates for Wednesday
Post Syndicated from jzb original https://lwn.net/Articles/1105378/
Security updates have been issued by AlmaLinux (cockpit, dpdk, fence-agents, firefox, freerdp, gimp, opentelemetry-collector, python-dns, qemu-kvm, and raptor2), Debian (apt and squid), Fedora (ags, apptainer, chromium, fractal, mingw-harfbuzz, mingw-qt5-qtwebkit, mingw-qt6-qt5compat, python-mistune, python3-docs, python3.14, python3.9, rubygem-gist, rust-app-store-connect, rust-qemu-rdp, rust-redlib, and selenium-manager), Mageia (java-latest-openjdk, java-17-openjdk, java-21-openjdk, timezone), Oracle (.NET 10.0, .NET 8.0, .NET 9.0, bind, bind9.16, cockpit, firefox, freerdp, gcc, ghostscript, glibc, grafana, java-17-openjdk, java-21-openjdk, kernel, kernel-uek, libXi, pipewire, pki-deps:10.6, podman, python-jwt, python-pillow, python-pyasn1, qt5-qtbase, thunderbird, tomcat, util-linux, and wireshark), Red Hat (dnsmasq, fence-agents, freerdp, pki-core:10.6, and thunderbird), SUSE (amazon-ssm-agent, aom-tools, apache2, brotli, cadvisor, chromium, cups, curl, distribution-registry, eog, gh, go-containerregistry, google-guest-agent, gvfs, haproxy, hauler, helm3, kernel, libBasicUsageEnvironment2, libcdio, libinstpatch-1_0-2, libosmocore, libreoffice, libX11, nodejs22, nvidia-open-driver-G06-signed, openssh, parted, perl-DBI, perl-mime-tools, python-pypdf, rootlesskit, rqlite, rsyslog, sssd, tomcat10, warewulf4, and xen), and Ubuntu (apt-cacher, bind9, bitlbee, cakephp, deluge, dmitry, e17, feh, gnome-shell, golang-github-gin-contrib-cors, gvfs, haproxy, jabberd2, libmspack, libnet-easytcp-perl, libphp-swiftmailer, libsoup2.4, libsoup3, libuser, pcre2, rear, ruby-rack, ruby-sprockets, rxvt-unicode, shapelib, sogo, vips, and yaws).
See the agents, set the terms: new visibility and control for personal agents
Post Syndicated from Marina Elmore original https://blog.cloudflare.com/personal-agents-visibility-control/
Personal agents are the intermediary between humans and the Internet, turning a person’s instructions into requests and actions on websites. A customer might ask a personal agent to compare products across your site, find support articles, or complete a purchase. To a site owner, all three interactions show up as automated traffic — and without a clear view of which agents are visiting and what they are doing, it can be difficult to know whether that traffic is helping your business or creating risk. Blocking agents altogether can feel like the safest choice, but it can mean losing customers. Better visibility into agent activity allows you to decide what access makes sense for your site.
Today, we’re launching new analytics to help you understand how personal agents access your site on behalf of humans, along with more granular access policies to put those decisions into practice. Together, they let you welcome agents on your own terms, and in ways that support your business.
See how agents access your site
Knowing which agent is behind a request turns unexplained automated traffic into traffic you can act on with confidence. Cloudflare maintains the largest verified bot directory in the world, and we are now bringing that intelligence into your traffic details. In Security Analytics, the Bot Analysis chart now shows Personal Assistants as a new category, next to Verified Bot, Likely Human, Likely Automated, and Automated. Security teams can select it to see only personal agent traffic over time.
In Top statistics, a new Personal Assistants widget lists which agents are visiting your site and how many requests each one sends. Filter on one agent and every other widget updates to show only its traffic details: the paths it requests, the status codes it receives, and the networks it comes from. At a glance, you can see whether an agent is logging in, reading your product pages, reaching your checkout, or hitting errors on pages it cannot use.
For sites that protect user accounts with Account Abuse Protection (currently in early access), site owners and fraud teams are able to see which user each agent represents. The population overview page shows which personal agents are active across your users and how many accounts use them, so you can determine whether agent traffic is a meaningful part of your business. Every login and sign-up event now shows whether a personal agent made the request, and which one. Fraud teams can filter accounts by AI assistant events or number of AI assistants.
Additionally, each user's account overview shows the agents acting for that account. A fraud analyst investigating an unusual login can tell whether it came from an agent the customer has relied on for weeks, or from an agent that appeared for the first time today and needs a closer look. If it looks like an attacker is using an agent on an account, fraud analysts can mitigate that account directly, with a WAF rule on its Hashed User ID, without blocking the agent for everyone else who relies on it.
Together, these views give you a clearer basis for deciding which personal agents to welcome, limit, or block.
Set access policies that reflect your preferences
We introduced AI bot policies this summer so site owners could make separate access control choices for AI bots used for Search, Training, and Agent behaviors. Now we’re expanding the existing Agents policy to include granular control options for supported personal agents. To reflect this broader scope, we’re renaming the setting AI Crawler and Agent access policies.
In Security Settings, you can set an overall Agents policy, then choose a different policy for each supported personal agent: Allow (do not block), Block on pages with ads, or Block. For example, you can set the overall Agents policy to Block on pages with ads, then choose Allow (do not block) for a supported personal agent you want to welcome. Your existing Search and Training policies stay as they are.
You can also make these choices when you add a new zone to Cloudflare. During onboarding, we ask whether you monetize pages with ads and then tailor the recommended policies to your answer. You can always revisit your access controls later in Security Settings.
The right policy depends on your site. One publisher may allow a supported personal agent throughout its site so readers can find its articles, while another may block that same agent on pages where ads support the content. Both publishers are choosing the access control that works for their business.
Agent identity is only part of the story
The analytics and policies we’re launching today give site owners visibility into personal agent activity and control over their access. Our next goal is to help site owners preserve the context of their relationships with users when personal agents act as intermediaries. A site may recognize the agent making a request but lack information it would otherwise have about the user: whether they are an existing customer, what they authorized the agent to do, whether they have a subscription, or which protections should apply.
Reaching that goal will require privacy-aware ways to (1) carry user context through an agent, (2) help sites assess reputation, and (3) establish clear accountability when something goes wrong. We’ll be sharing more as we work with agent operators and others across the ecosystem, so site owners can choose whether to grant agents greater access while continuing to build relationships with their users.
Make the choice for your site
That person asking a personal agent to compare products, find support, or complete a purchase is still a customer trying to reach your business. Review how personal agents are accessing your site, then visit Security Settings → AI Crawler and Agent access policies to set the terms that work for your site.
Best of The History Guy: Mighty Beasts
Post Syndicated from The History Guy: History Deserves to Be Remembered original https://www.youtube.com/watch?v=WYgmmzBMu1Y
‼️ PRODUCT LAUNCH – No device left behind 🔌
Post Syndicated from Home Assistant original https://www.youtube.com/watch?v=YpcrIy5f774
Celebrating the UK’s National Engineering Day 2026
Post Syndicated from Philippa Hanman original https://www.raspberrypi.org/blog/celebrating-the-uks-national-engineering-day-2026/
We’re celebrating National Engineering Day in the UK with our friends at the Royal Academy of Engineering. National Engineering Day aims to make the UK’s engineers and engineering more visible, and celebrate how they improve everyday lives and shape the world around us.
Now hiring: The engineers of 2076
This year, the Royal Academy of Engineering is marking its 50th anniversary by looking 50 years into the future. Through job ads for roles that don’t exist yet, they invite us to imagine the engineering careers that will build life on the Moon, Mars, and beyond.
Scientific investigations in space
Some of those future engineers could be taking their first steps today. They might be getting their first experience with space science in the European Astro Pi Challenge, for example. This ESA Education project is run in collaboration with the Raspberry Pi Foundation and offers young people the amazing opportunity to conduct scientific investigations in space by writing computer programs that run on Raspberry Pi computers aboard the International Space Station (ISS).
We spoke to Geraint Ballinger, a Software Development and Deployment Engineer who works on the Astro Pi Challenge, to find out what engineering roles he thought could be important in the future. We also discussed how the engineers of 2076 need opportunities to experiment, solve problems, and build confidence today.
Hi Geraint. Can you tell us a bit about your role as a Software Development and Deployment Engineer at the Raspberry Pi Foundation?
I like to describe it as a blend between traditional software engineering and teaching. The overall aim of my work is to help young people run code on the Astro Pi computers aboard the International Space Station, which means designing systems that hide unnecessary complexity so students can learn and solve problems effectively, while ensuring the software deployed to orbit remains secure and compliant.
Part of the role is to create applications and code libraries that young people can use to simplify the routine things so they can focus their energy on the interesting aspects of running code in space: taking pictures of the Earth and investigating various scientific concepts. I also oversee the pipeline that receives their work — reviewing submissions, moderating Mission Zero images, and building internal tools to streamline the review process.
On the flight software side, I am jointly responsible for delivering the Astro Pi operating system on the ISS. This involves preparing and delivering system updates, coordinating security reviews, and developing internal astronaut-facing applications such as the application used by the astronauts to focus the Astro Pi cameras.
What do you most enjoy about your role?
I enjoy the sheer variety of engineering challenges to which I am exposed. In any given week, I might be writing a Python library, developing a Typescript web application, or diagnosing a low-level hardware failure on the ISS — like debugging corrupted SD cards. In particular, I have really enjoyed the challenge of maintaining a system on real physical hardware in space. Operating a Raspberry Pi in orbit makes it impossible to ignore the physical machine: you have to actively design around constraints such as solar radiation, tight power and bandwidth budgets, and hardware degradation over the mission lifecycle. It’s been really interesting to learn about the procedures and processes involved in delivering software and hardware into orbit.
How does your work help young people’s Astro Pi programs run on the ISS?
I developed the Astro Pi Replay tool, an online browser emulator that simplifies testing and code submission for Mission Space Lab. This allows anyone with a standard school laptop to test their code as if it were running on the ISS, without the need for physical hardware.
Alongside the software tooling, I am also involved in writing the educational materials that guide young people and mentors through the core concepts required for Mission Space Lab. These resources hopefully enable participants to get up to speed quickly, and to produce working code within a few hours.
What skills do you see young people practising through Astro Pi that future space engineers will need?
Problem-solving, patience, critical thinking, and creativity are vital skills for future space engineers that young people put into practice through the Astro Pi Challenge.
In Mission Space Lab, the more advanced of the Astro Pi missions, young people learn to break down complex tasks into manageable pieces and to coordinate independent pieces of work as a team.
Becauses technical failures and software bugs are inevitable realities of operating in space, Mission Space Lab gives participants practical opportunities to hone their debugging skills, to build resilience and a constructive approach to problem-solving, and foster an active curiosity about underlying system processes.
National Engineering Day is imagining the engineers of 2076. What space engineering job would you invent, and what would someone need to know or be able to do to succeed in it?
I’d invent the role of Interplanetary Communications Manager. If we’ve reached Mars by 2076, then keeping a reliable link back to Earth will be critical infrastructure, and someone will need to look after it.
The job would sit across software and hardware. Software will be a big part of it, but you’d always be working with physical systems, particularly radio transmission. I don’t think we’ll find a fundamentally new way to communicate across space, so I’d expect the role to build on radio and optical technology we already use today. So the key knowledge would be the physics of communication, such as how radio waves and light travel over huge distances, along with how networks are designed to stay reliable.
I also expect AI to touch almost every area of engineering, but I doubt something this critical (and expensive!) would be left entirely without human oversight. There will always be a need for people who truly understand how the system works and can judge whether it can be trusted. That understanding is what I’d want a candidate to bring to the role.
Thanks, Geraint! And we hope any future Interplanetary Communications Managers try out the Astro Pi Challenge, which is open for submissions now!
Get involved with National Engineering Day
Now it’s your turn. What engineering role would you create for 2076? Find out more about how to take part on the Royal Academy of Engineering website.
And if your young people and future engineers would like to enter the European Astro Pi Challenge 26/27, visit: https://astro-pi.org/ to select a mission.
The post Celebrating the UK’s National Engineering Day 2026 appeared first on Raspberry Pi Foundation.
Anne Applebaum on the Future of American Democracy
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=ofOnmMiI0A8
AMD Q3 2026 Earnings Data Center Growth Drives Record Quarter
Post Syndicated from Cliff Robinson original https://www.servethehome.com/amd-q3-2026-earnings-data-center-growth/
AMD Q3 2026 earnings were massive with the data center and embedded segments seeing big uplift with the clear Venice x86 leadership looming
The post AMD Q3 2026 Earnings Data Center Growth Drives Record Quarter appeared first on ServeTheHome.
What’s Still Missing From the ZR After 2.00
Post Syndicated from Matt Granger original https://www.youtube.com/watch?v=Cw3OW4mzUDk
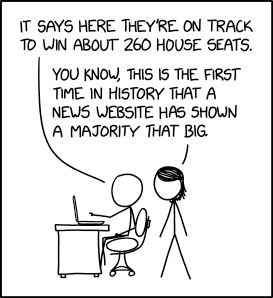
House Majority
Post Syndicated from xkcd.com original https://xkcd.com/3320/
I Built a Network Activity Display Out of Smart Lights
Post Syndicated from Crosstalk Solutions original https://www.youtube.com/shorts/H1GmLNQLc5k
Three Tips for Watching the Results Roll In
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/Kinc4Ek7mK8
Republicans & James Talarico #lastweektonight
Post Syndicated from LastWeekTonight original https://www.youtube.com/shorts/KcK_EIEODJE
OpenSUSE Leap 16.1
Post Syndicated from daroc original https://lwn.net/Articles/1105131/
The openSUSE project has announced the release of openSUSE Leap 16.1. The release is notable for allowing both traditional installations and immutable images with transactional updates. While immutable images had previously been available for Leap Micro, they are now available across all platforms that Leap supports, including servers, desktops, and virtual machines.
“Leap’s image gives the best of both for traditional and immutable users, and we expect that Tumbleweed will follow when Agama becomes the default installer for Tumbleweed as well.” said Leap release manager Lubos Kocman. “The Leap Micro experience people relied on is still here, but now it shares the same release, the same life cycle and the same maintenance updates as the rest of Leap, so users only have to pick the mode that fits their workload.”
Republicans & Abdul El-Sayed #lastweektonight
Post Syndicated from LastWeekTonight original https://www.youtube.com/shorts/4RoLmhoLdRQ
[$] LLM reviews for Debian’s new queue spark debate
Post Syndicated from jzb original https://lwn.net/Articles/1103674/
The Debian project has wrestled with the topic of LLM usage for years, which
culminated in a general-resolution
vote this August. The project voted in favor of the fifth, out of
eight, option: “Responsible Use of
Generative AI“. With the door open to LLM use, the DFSG, Licensing & New Packages
Team (usually shortened to “DFSG team”), which is relatively new, has started to employ LLMs in
sending out reviews of packages entering Debian’s new queue. The practice has
raised a number of objections and questions about where lines should be drawn in
the use of LLM-generated output.
Fedora Linux 45 released
Post Syndicated from jzb original https://lwn.net/Articles/1105121/
Fedora Linux
45 has been released. This includes all editions: Fedora Workstation, Fedora KDE Plasma Desktop, Fedora Server, Fedora Cloud, Fedora CoreOS, and Fedora IoT, as well as the Atomic Desktops and Spins.
This release adds support for installation
on Stratis storage using Anaconda or Kickstart installs, retires
unmaintained VPN plugins for NetworkManager, and updates Fedora’s desktop
environments, developer toolchains, and system packages. See the Fedora wiki
ChangeSet page for a list of major changes.