Post Syndicated from xkcd.com original https://xkcd.com/2899/
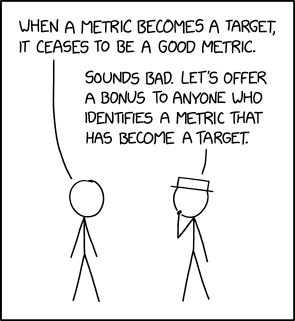
Post Syndicated from xkcd.com original https://xkcd.com/2899/
Post Syndicated from LastWeekTonight original https://www.youtube.com/watch?v=PbzW9qcVBJ0
Post Syndicated from LastWeekTonight original https://www.youtube.com/watch?v=_m4JMTixTTM
Post Syndicated from turnoff.us original http://turnoff.us/geek/sexrobot-2024/
Post Syndicated from Matt Granger original https://www.youtube.com/watch?v=1HwAvljNCZ4
Post Syndicated from Explosm.net original https://explosm.net/comics/clipboard
New Cyanide and Happiness Comic
Post Syndicated from Oglaf! -- Comics. Often dirty. original https://www.oglaf.com/mystery/


Post Syndicated from Geographics original https://www.youtube.com/watch?v=ne63LEGGYWw
Post Syndicated from Patrick Kennedy original https://www.servethehome.com/farewell-brave-8tb-wd-hard-drive-you-served-sth-well/
We finally removed this brave 8TB WD sucked hard drive from the hosting array. It had an interesting life and helped STH in many ways
The post Farewell Brave 8TB WD Hard Drive You Served STH Well appeared first on ServeTheHome.
Post Syndicated from turnoff.us original http://turnoff.us/geek/deadline-2/
Post Syndicated from Techmoan original https://www.youtube.com/watch?v=Uejdf_XTBT0
Post Syndicated from Надежда Радулова original https://www.toest.bg/sedmitsata-19-24-fevruari/

Почти седмица след обявяването на смъртта на Алексей Навални тялото му се намираше в неизвестност, или по-точно в известност само за определени лица в Русия, „администриращи“ тази смърт и последиците от нея. Макар че преди два дни майката на Навални най-сетне е била допусната да види тялото, то все още не е „освободено“, а властите посредством заплахи настояват на тайно погребение.
Това, разбира се, е непростимо според всички писани и неписани закони, конвенции, практики… Или може би Путин, изживявайки се като Зевс, очаква да бъде изрично помолен да разпореди връщането на вражеските тленни останки. Точно както в „Илиада“ – именно чрез намесата на Зевс – Приам успява да „откупи“ тялото на загиналия Патрокъл. Нищо красиво, още по-малко възвишено няма в тези руски игри на митологии. Все същата хищна, гнусна, човеконенавистна вседържавна машина, която третира поданиците си като крепостни и ги праща да гният в Сибир или да мрат по фронтовете в кръвопролитни войни.
В памет на враг номер едно на Владимир Путин и режима му публикуваме биографичния очерк „In memoriam: Алексей Навални“. В него Йоанна Елми подробно ни запознава с живота и борбите на политика и опозиционера, когото диктатурата в Русия уби, но убивайки го, създаде условия да бъде „канонизиран“.
Извън тази основна в новините тема от последната седмица, четете в броя още:
И за да се върнем отново в темата на седмицата, без да напускаме полето на поезията и на хулиганството, чуйте прословутата „епиграма“ от Осип Манделщам „Мы живем, под собою не чуя страны…“, написана през 1933 и посветена на Сталин (наречен в текста „планинец“ и „осетинец“). Заради нея поетът е арестуван и впоследствие изпратен на заточение. Нищо ново под слънцето, ще кажете. Но добър повод да си припомним, че в земите и времената на непоклатимите диктатори поезията може да бъде и форма на съпротива.
Post Syndicated from Explosm.net original https://explosm.net/comics/friended
New Cyanide and Happiness Comic
Post Syndicated from John Lee original https://www.servethehome.com/arm-neoverse-s3-detailed-for-the-infrastructure-chiplet-era/
The Arm Neoverse S3 with the CMN S3, MMU S3, and NoC S3 underpin the company’s new Neoverse CSS offerings for future chiplet based processors
The post Arm Neoverse S3 Detailed for the Infrastructure Chiplet Era appeared first on ServeTheHome.
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=930jCXFL0M4
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/02/friday-squid-blogging-illex-squid-and-climate-change.html
There are correlations between the populations of the Illex Argentines squid and water temperatures.
As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.
Read my blog posting guidelines here.
Post Syndicated from corbet original https://lwn.net/Articles/963444/
Version 2.44.0 of the Git
source-code management system has been released. There is a long list of
changes, including the git
replay command for faster, server-side rebasing, a number of
command-line completion improvements, and more.
Post Syndicated from jzb original https://lwn.net/Articles/963095/
The world of open-source “forges” is becoming a little more fragmented. The Forgejo project is a software-development platform that started as a “soft
” fork of Gitea in late 2022. On February 16, Forgejo announced its intent to become a “hard fork
” of Gitea to help address its mission of community-controlled development and to “liberate software development from the shackles of proprietary tools
“. In a world where proprietary tools cast a long shadow over open-source development that’s a welcome sentiment—if the project can deliver.
Post Syndicated from Home Assistant original https://www.youtube.com/watch?v=Jxup-fKFpfs
Post Syndicated from Spencer McIntyre original https://blog.rapid7.com/2024/02/23/metasploit-weekly-wrap-up-02-23-2024/
Metasploit now has an LDAP capture module thanks to the work of llcjngdjttrvddchfntdbinjblktjjetrtifdlibuchh
JustAnda7. This work was completed as part of the Google Summer of Code program.
When the module runs it will by default require privileges to listen on port 389. The module implements a default implementation for BindRequest, SearchRequest, UnbindRequest, and will capture both plaintext credentials and NTLM hashes which can be brute-forced offline. Upon receiving a successful Bind Request, a ldap_bind: Authentication method not supported (7) error is sent to the connecting client.
The module can be with run:
msf6 > use auxiliary/server/capture/ldap
msf6 auxiliary(server/capture/ldap) > run
Incoming requests will have their credentials stored for later use:
[+] LDAP Login attempt => From:10.0.2.15:48198 Username:User Password:Pass
[+] LDAP Login Attempt => From:127.0.0.1:55566	 Username:admin	 ntlm_hash::8aa0e517cd547b4032ff7e9c5359c200879aa5a8031d3d74	 Domain:DOMAIN
These values will be stored in the database for later retrieval:
msf6 auxiliary(server/capture/ldap) > creds
Credentials
===========
host       origin     service         public  private  realm        private_type  JtR Format
----       ------     -------         ------  -------  -----        ------------  ----------
10.0.2.15  10.0.2.15  389/tcp (ldap)  User    Pass     example.com  Password
Another honorable mention for this week’s Metasploit release is a module by sfewer-r7 that chains two recently disclosed vulnerabilities(CVE-2024-21893 and CVE-2024-21887) in Ivanti gateways to achieve remote code execution on a vulnerable target. The vulnerabilities are both being widely exploited in the wild. Read Rapid7’s full technical analysis of the exploit chain in AttackerKB.
Author: JustAnda7
Type: Auxiliary
Pull request: #18678 contributed by jmartin-tech
Path: server/capture/ldap
Description: Adds a new auxiliary/server/capture/ldap module that emulates an LDAP Server. The server accepts a user’s bind request, and the user credentials or NTLM hash is then captured, logged, and persisted to the currently active database. An ldap_bind: Authentication method not supported (7) error is sent to the connecting client.
Author: sfewer-r7
Type: Exploit
Pull request: #18792 contributed by sfewer-r7
Path: linux/http/ivanti_connect_secure_rce_cve_2024_21893
AttackerKB references: CVE-2024-21887, CVE-2023-36661, CVE-2024-21893
Description: This module exploits the recently disclosed SSRF vulnerability (CVE-2024-21893) in Ivanti Connect Secure and Ivanti Policy Secure. The SSRF is chained to a command injection vulnerability (CVE-2024-21887) to achieve unauthenticated RCE.
Authors: BobTheShopLifter and Thingstad and h00die-gr3y [email protected]
Type: Exploit
Pull request: #18700 contributed by h00die-gr3y
Path: linux/http/kafka_ui_unauth_rce_cve_2023_52251
AttackerKB reference: CVE-2023-52251
Description: This PR adds an exploit module for a command injection vulnerability that exists in Kafka-ui between v0.4.0 and v0.7.1 that allows an attacker to inject and execute arbitrary shell commands via the groovy filter parameter at the topic section.
Authors: Spencer McIntyre, jheysel-r7, and sfewer-r7
Type: Exploit
Pull request: #18832 contributed by sfewer-r7
Path: linux/http/qnap_qts_rce_cve_2023_47218
AttackerKB reference: CVE-2023-47218
Description: The PR adds a module targeting CVE-2023-47218, an unauthenticated command injection vulnerability affecting QNAP QTS and QuTH Hero devices. CVE-2023-47218 was discovered and disclosed by Stephen Fewer.
Modules which have either been enhanced, or renamed:
Simple Authentication attempts. When launching this module with default options users must have permissions to bind to port 389.BindRequest, SearchRequest, UnbindRequest, as well as a default action for unsupported requests.options command. This will be for modules that support either an RHOST or a SESSION connection to show that only one or the other is required when using the new session type features for SMB/MSSQL/MYSQL/PostgreSQL sessions.postgres_login module.mssql_login module.mysql_login module.cwd convention from SQL-based sessions, and instead uses a more appropriate def database_name computed value rather than a cached variable.ENVCHANGE types to the MSSQL client mixin, and uses those to fetch the initial DB name received from the server.ls and dir inside SMB sessions.features set postgresql_session_type true command.You can always find more documentation on our docsite at docs.metasploit.com.
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro