Tag Archives: Vector Command

A Day With Your Vector Command Red Team Pod

Post Syndicated from Trevor Christiansen original https://www.rapid7.com/blog/post/so-ditl-day-with-your-vector-command-red-team-pod

Anyone trying to understand continuous red teaming usually gets the same high-level explanation: it is ongoing, attacker-informed, and designed to uncover risk between formal assessments. Useful as that description is, it still leaves most people with the same question, which is what the service actually looks like when a team is working against a real environment day after day.

A Vector Command pod answers that question more clearly than a list of features ever could. Five dedicated operators work against a customer environment continuously, each bringing a different specialty, while the pod as a whole simulates the range, coordination, and persistence of a real adversary. Over time, that gives the customer far more than a periodic snapshot. It gives them a team that keeps learning the environment, keeps pressure on the attack surface, and keeps surfacing the kinds of changes that can turn into incidents if no one catches them quickly.

Because the environment keeps changing, the value of the model shows up in motion rather than in theory. New services appear, controls drift, patching gaps open, and fresh advisories create short windows of risk. Working continuously allows the pod to validate whether those changes matter while they are still actionable, which is what makes the service useful to teams that want more than another point-in-time assessment.

How the Red-Teaming pod works across a normal day

Every day begins with a 30-minute standup, where operators compare notes on what is in motion, what has already been found, and where handoff is needed. That routine may sound simple, but it is what turns five specialists into a coordinated attack team instead of a set of separate testing tracks.

While one operator follows a foothold on a build server, another may be preparing a social engineering campaign tied to a real business event. At the same time, someone else is watching the external footprint for fresh exposures, an emerging threat specialist is validating a new advisory against active customer technology, and the customer interface lead is already helping a security team understand what yesterday’s compromise means in practical terms. The customer is not seeing isolated tasks. They are seeing multiple attack paths, exposure checks, and validation efforts develop at once, with the work feeding into a single picture of risk.

Because the pod works across multiple attack paths at once, the value comes through in more than the sheer volume of activity. Familiarity builds over time, and that accumulated knowledge changes the quality of the work by grounding the findings in how the customer’s environment actually behaves.

What customers are actually getting tested

One of the clearest examples in the draft comes from the lead operator, who receives a callback from a beacon on a customer’s build server and begins exploring what that foothold could reach. Because the build server holds CI/CD credentials, the question is no longer whether the server can be compromised. The more important question is whether that compromise could extend into the deployment pipeline and what persistence would look like from there. For the customer, that kind of work shows how a technical foothold could become a business problem, which is much more useful than a simple proof that access was achieved.

The social engineering work gives a different kind of visibility. Domains are warmed, pretexts are built around real events, target lists are researched carefully, and emails are tested against spam controls before launch. That means the customer is not just testing whether an employee clicks a link. They are testing the full defensive chain, including email filtering, web controls, endpoint visibility, and SOC response.

Continuous external testing tends to make the value especially obvious. In the draft, the network and vulnerability operator identifies two RDP endpoints that are brand new to a customer’s environment and gets them in front of the customer the same day they appear. He also finds a Confluence instance several versions behind and confirms unauthenticated remote code execution. Those are the kinds of issues that often emerge between scheduled assessments and create risk precisely because no one expected them to be there.

When a fresh advisory lands against an exposed technology, the value of the service becomes even clearer. Broad awareness of an industry issue only goes so far. What changes the customer’s decision is knowing whether the exposure is exploitable in their own environment and what an attacker could reach from there.

Where the customer benefit becomes tangible

A service like this becomes much easier to understand when the output is viewed through the customer’s side of the experience. Early visibility into configuration drift, newly exposed services, lagging systems, and fresh exploit windows helps teams focus on changes that are real rather than theoretical. Validation tied to the customer’s own environment gives them a stronger basis for deciding what needs immediate attention. Attack-path testing shows how one weakness could become a wider compromise. Practical remediation guidance helps leadership and technical teams respond while the timing still matters.

Because the customer interface lead is also an operator, the translation from technical finding to leadership action is grounded in hands-on work rather than abstract summary. When a foothold, exposed service, or confirmed compromise needs to be explained, the conversation can move quickly from what happened to what the customer should prioritize next.

Over time, customers get more than a stream of findings because the pod is building familiarity with the environment as it works. That continuity gives the team a stronger basis for identifying which exposures deserve urgent attention, which attack paths are credible, and which changes are likely to matter most if an adversary finds them first.

Why this model gives customers more than a snapshot

Point-in-time testing still has value, but it will always be limited by the fact that the environment keeps moving after the engagement ends. A continuous pod keeps pace with that reality more effectively because it maintains pressure on the environment as it changes, rather than returning periodically to rediscover what is there.

Customers who want a clearer view of what continuous red teaming looks like in practice are really looking for evidence that the model changes the quality of what they get back. A dedicated pod does that by combining sustained offensive pressure, environment familiarity, rapid validation, and practical remediation guidance in a way that helps teams act on real risk while the timing still matters.

For organizations exploring how to test more continuously against the way attackers actually operate, Rapid7’s Continuous Red Team Service offers a closer look at how Vector Command helps uncover attack paths, validate exposures, and strengthen resilience over time.
Red Teaming in 2026: What to Expect at our 2026 Global Cybersecurity Summit

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/it-red-teaming-2026-global-cybersecurity-summit

Red teaming has always played a role in testing defenses, but in 2026 its role is changing. Security teams are no longer asking whether an attacker can get in. That question has already been answered. The real challenge is whether teams can detect, validate, and respond before an incident escalates.

That shift sits at the center of this year’s Rapid7 Global Cybersecurity Summit, taking place on May 12-13. As part of the Continuous Threat Defense pillar, the summit will explore red teaming not as a standalone exercise, but as a core input into how modern security operations function day to day.

From validation to continuous feedback

In sessions like Using Red Teaming to Power Preemptive MDR, the focus moves away from point-in-time testing and toward becoming part of a continuous feedback loop. Detection logic is tested against real attacker techniques and gaps are exposed before they become incidents. Response workflows are refined in conditions that reflect how attacks actually unfold, rather than how they are expected to behave.

This represents a clear shift from traditional engagements. Instead of producing a static report, red teaming feeds directly into detection engineering and MDR operations. Many teams still rely on assumptions about coverage, but those assumptions often break down under pressure. Continuous validation helps close that gap.

Aligning red teaming with how attacks really happen

Modern attacks rarely follow a clean path. They move across identity, cloud, and endpoint, taking advantage of timing, visibility gaps, and delayed decisions. Red teaming has to reflect that reality.

At the summit, the conversation connects adversary behavior with how detection and response teams operate in practice. This includes how signals are correlated across environments, how escalation decisions are made, and where teams lose time during an investigation. The goal is not to simulate attacks for the sake of it, but to understand how those attacks would be detected, prioritized, and contained in a real environment.

Why red teaming matters now

The move toward preemptive security operations depends on confidence. Teams need to know that what they have built will hold up when it matters. Red teaming supports that by grounding security programs in evidence. It shows what works, highlights what does not, and gives teams an opportunity to improve before a live incident forces change.

This becomes even more important as organizations adopt MDR models, integrate AI into workflows, and operate across increasingly complex environments. Without continuous validation, complexity creates blind spots that are difficult to see until it is too late.

Rapid7’s Cybersecurity Summit: A preview of what’s to come

Red teaming is one part of a broader shift happening across the summit. Sessions across detection, response, AI, and exposure management all point in the same direction: Security operations must move earlier in the attack lifecycle, reduce noise, improve prioritization, and support faster decisions with better context.

More sessions and speakers will be announced in the coming weeks, building out how this shift is being applied in practice. If you are responsible for detection, response, or validation of your security program, this is a conversation worth being part of.

Join us May 12–13 and see how teams are using red teaming to strengthen modern security operations.

Register now.

From Vectors to Verdicts: Web App Testing with Vector Command

Post Syndicated from Ed Montgomery original https://www.rapid7.com/blog/post/pt-vectors-verdicts-web-app-testing-vector-command

If it’s online, it’s a target

Web applications are no longer just business enablers, they’re often the front door to an organization. They can often generate revenue, enforce identity, connect systems and hold customer and business data.

75% of successful Vector Command breaches were conducted through web apps.Principal Security Consultant, Vector Command Team at Rapid7

From SaaS platforms and identity providers to customer portals and internal tools, attackers increasingly rely on web applications as their initial access point. In fact, application-driven attacks account for a significant percentage of real-world breaches. But testing web applications for real risk isn’t the same as scanning for bugs; that’s where Vector Command (Rapid7’s continuous managed red team service) comes in.

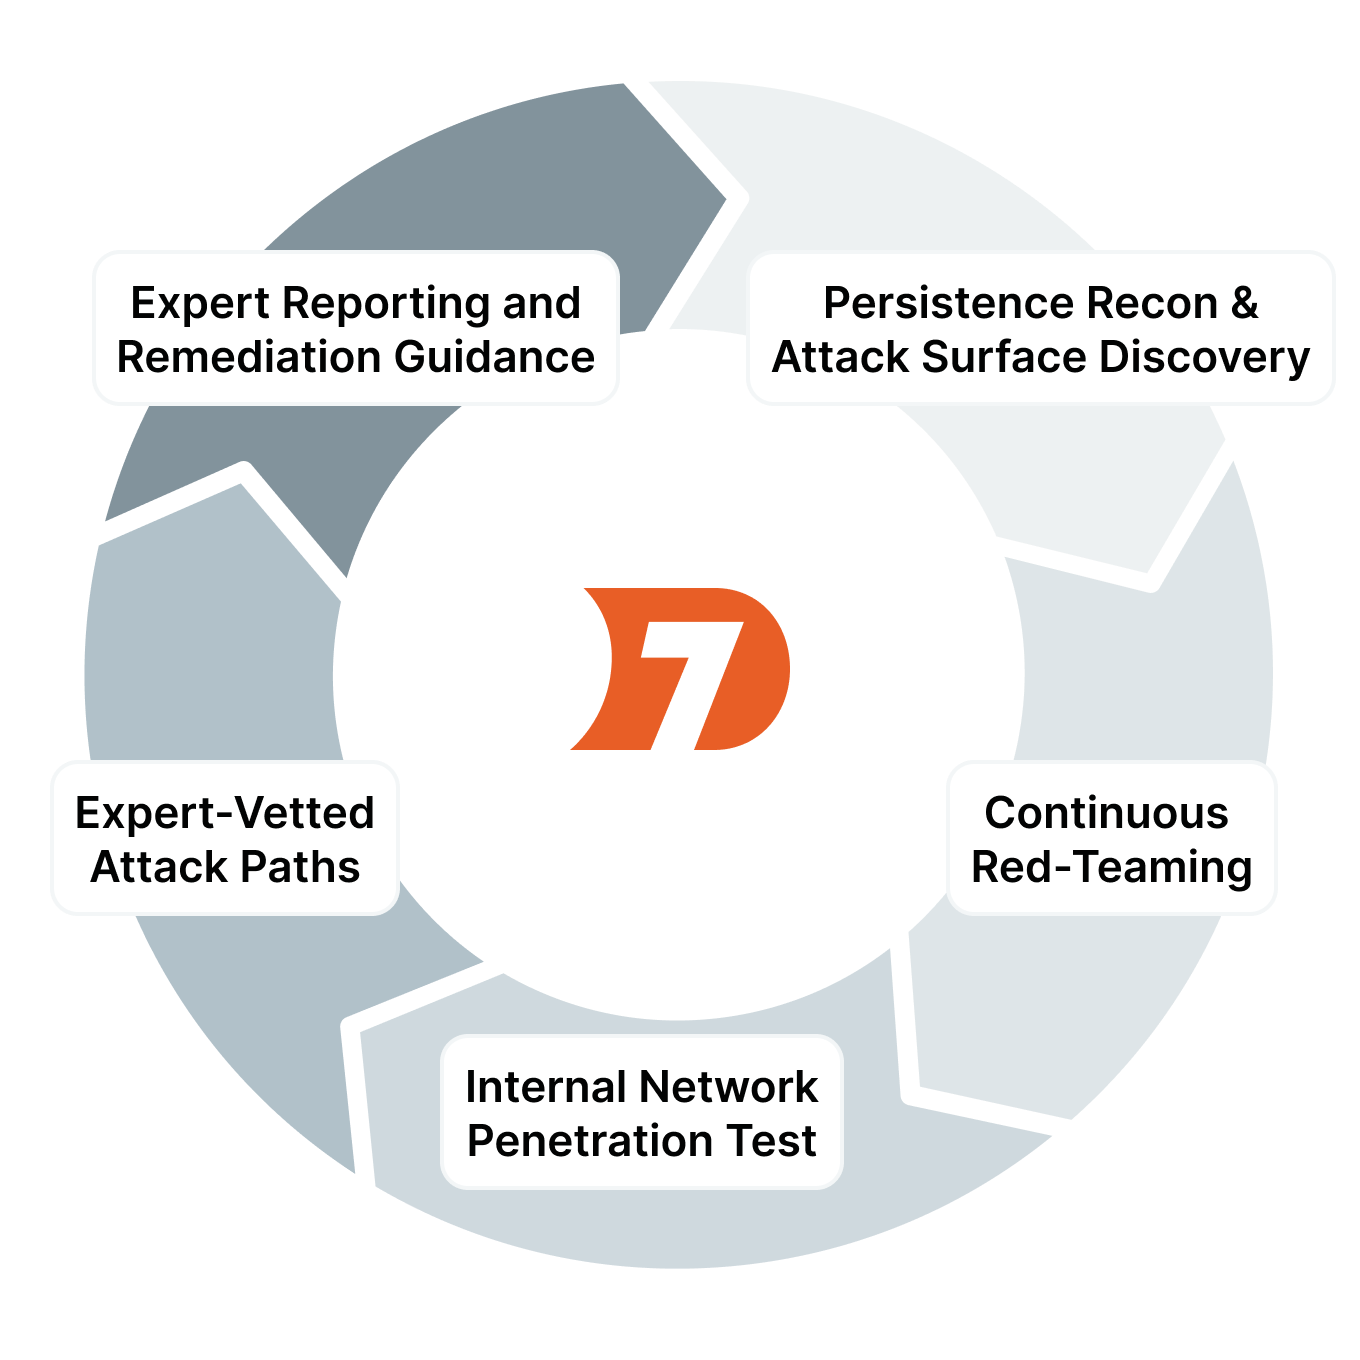
Rapid7-Vector-Command-Advanced.png
Figure 1: Vector Command Advanced

How Vector Command approaches web applications

Vector Command evaluates web applications the same way real attackers do, by asking a single question: Can this application be used to meaningfully compromise the organization?

Rather than attempting to enumerate every possible vulnerability, Vector Command focuses on exploitation paths that lead to real outcomes, such as:

  • Account takeover

  • Session hijacking

  • Abuse of SaaS trust relationships

  • Access to internal systems through vulnerabilities, such as malicious file uploads, injection issues, or misconfigurations in common web frameworks

  • Lateral movement across applications

  • Exfiltration of source code, if found during a breach

Testing begins without authentication against externally facing applications, the external attack surface, or to put it another way, what a potential threat actor can see. If legitimate paths exist – self-registration, broken authentication and authorization controls, misconfigurations exposing unintended application functionality, or overall poor site hygiene leaking information that needs further research – those paths are pursued as part of a broader attack chain.

The result isn’t a long list of low-risk findings, but rather a clear picture of what actually works.

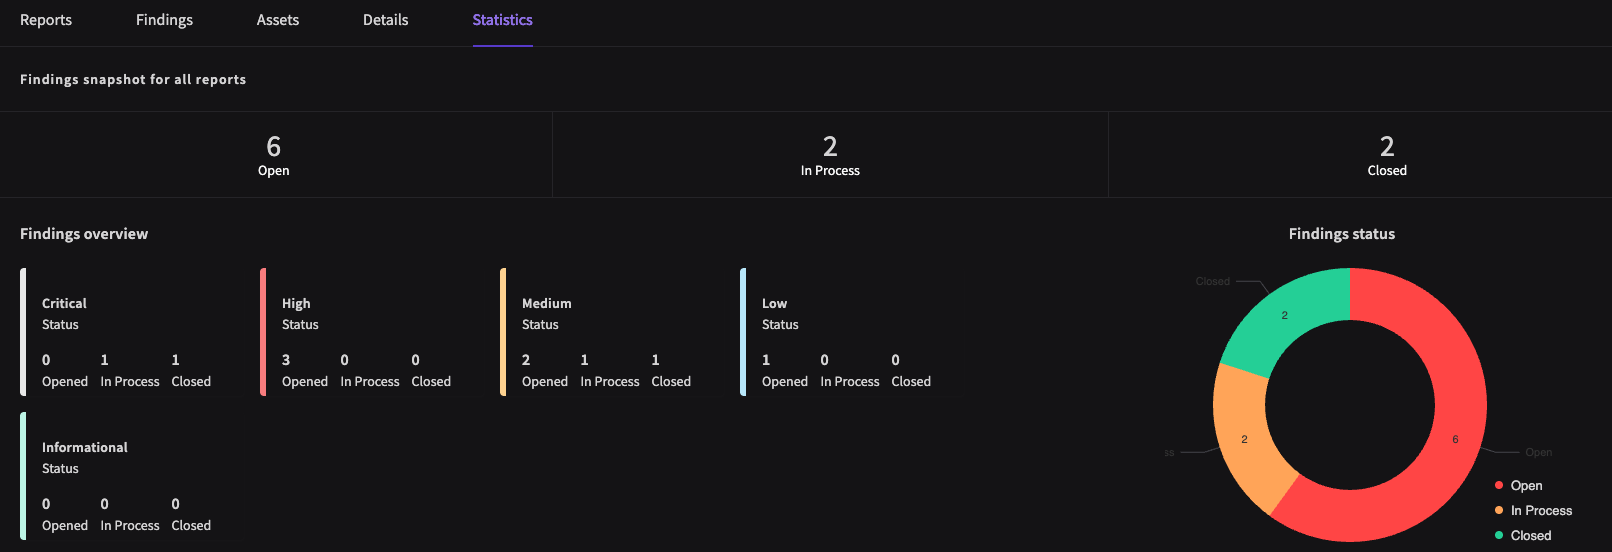
Rapid7-Sample-Vector-Command-findings.png
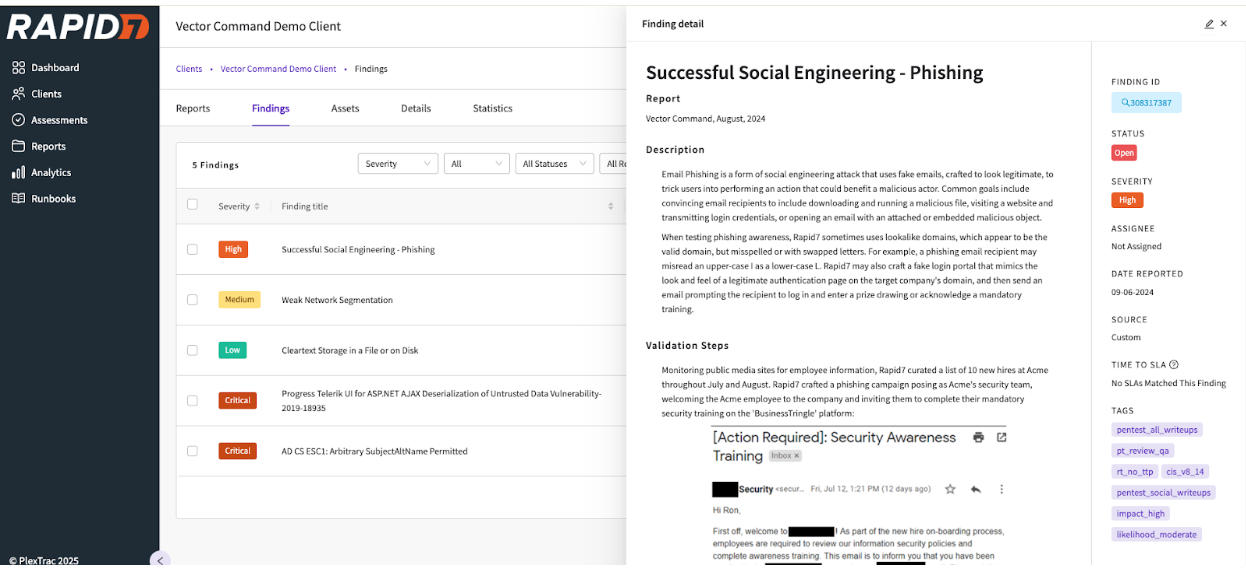
Figure 2: Sample Vector Command findings, by status

What Vector Command does not do

Vector Command is intentionally not a replacement for a full web application penetration test, although Rapid7 does offer this service.

It does not:

  • Guarantee full application coverage.

  • Perform DAST or SAST scanning.

  • Enumerate non-exploitable low-severity or theoretical vulnerabilities.

  • Review source code unless it’s obtained during an attack.

If your goal is to understand every potential flaw in an application, a dedicated web app penetration test is the right approach. However if your goal is to understand whether your sprawling stack of externally facing applications can be used to break into your organization, Vector Command is designed for that purpose.

A real-world example: when the ticketing system becomes the attack path

In one recent Vector Command engagement, attackers didn’t exploit a zero-day or complex vulnerability.

Instead, they targeted an externally accessible and very popular, SaaS ticketing portal used by IT. Through a well-placed social engineering attempt, they gained access to an internal support workflow. Any organization could register for the customer’s SaaS deployment, which was used to host IT documentation and their ticketing system.

The Vector Command team submitted a ticket to the customer’s IT team, seeking assistance to help fix an application installation issue. A SharePoint URL was provided to IT to view the software documentation, however… This SharePoint site was a proxy phishing portal, created by our Vector Command experts, designed to capture Office365 login sessions and the user’s MFA prompts. 

Hook, line and cookie: the result?

The unsuspecting IT help-desk employee had been phished and was convinced to run the Rapid7 payload, giving our Vector Command team access. The engagement demonstrated how easily trust relationships could be abused. From there, a malicious link led to session capture within a trusted collaboration platform.

  • Account takeover

  • Session theft

  • Lateral movement using legitimate tools

  • Access granted without triggering traditional defenses

No single “critical bug” caused the breach. It was the interaction between applications, identity, and trust that made it possible. That’s exactly the kind of risk Vector Command is designed to uncover and each one of our red team members has a particular speciality, when used together, they are formidable. 

Vector Command and web app pentesting: better together

Vector Command and web application penetration testing serve different, but complementary purposes. Web app pentests help teams build more secure applications, while Vector Command helps teams understand how those applications affect real-world security exposure.

One improves code; the other tests assumptions.

A final thought

Vector Command doesn’t try to answer “What could be wrong?”, answering instead, “What would actually succeed?”

Modern breaches rarely hinge on a single critical bug. They succeed because trusted systems interact in ways no one has validated.Vector Command tests those assumptions, continuously.

Purple Teaming in 2026: From Assumed Protection to Measurable Resilience

Post Syndicated from Aaron Herndon original https://www.rapid7.com/blog/post/so-purple-teaming-assumed-protection-to-measurable-resilience

What is purple teaming?

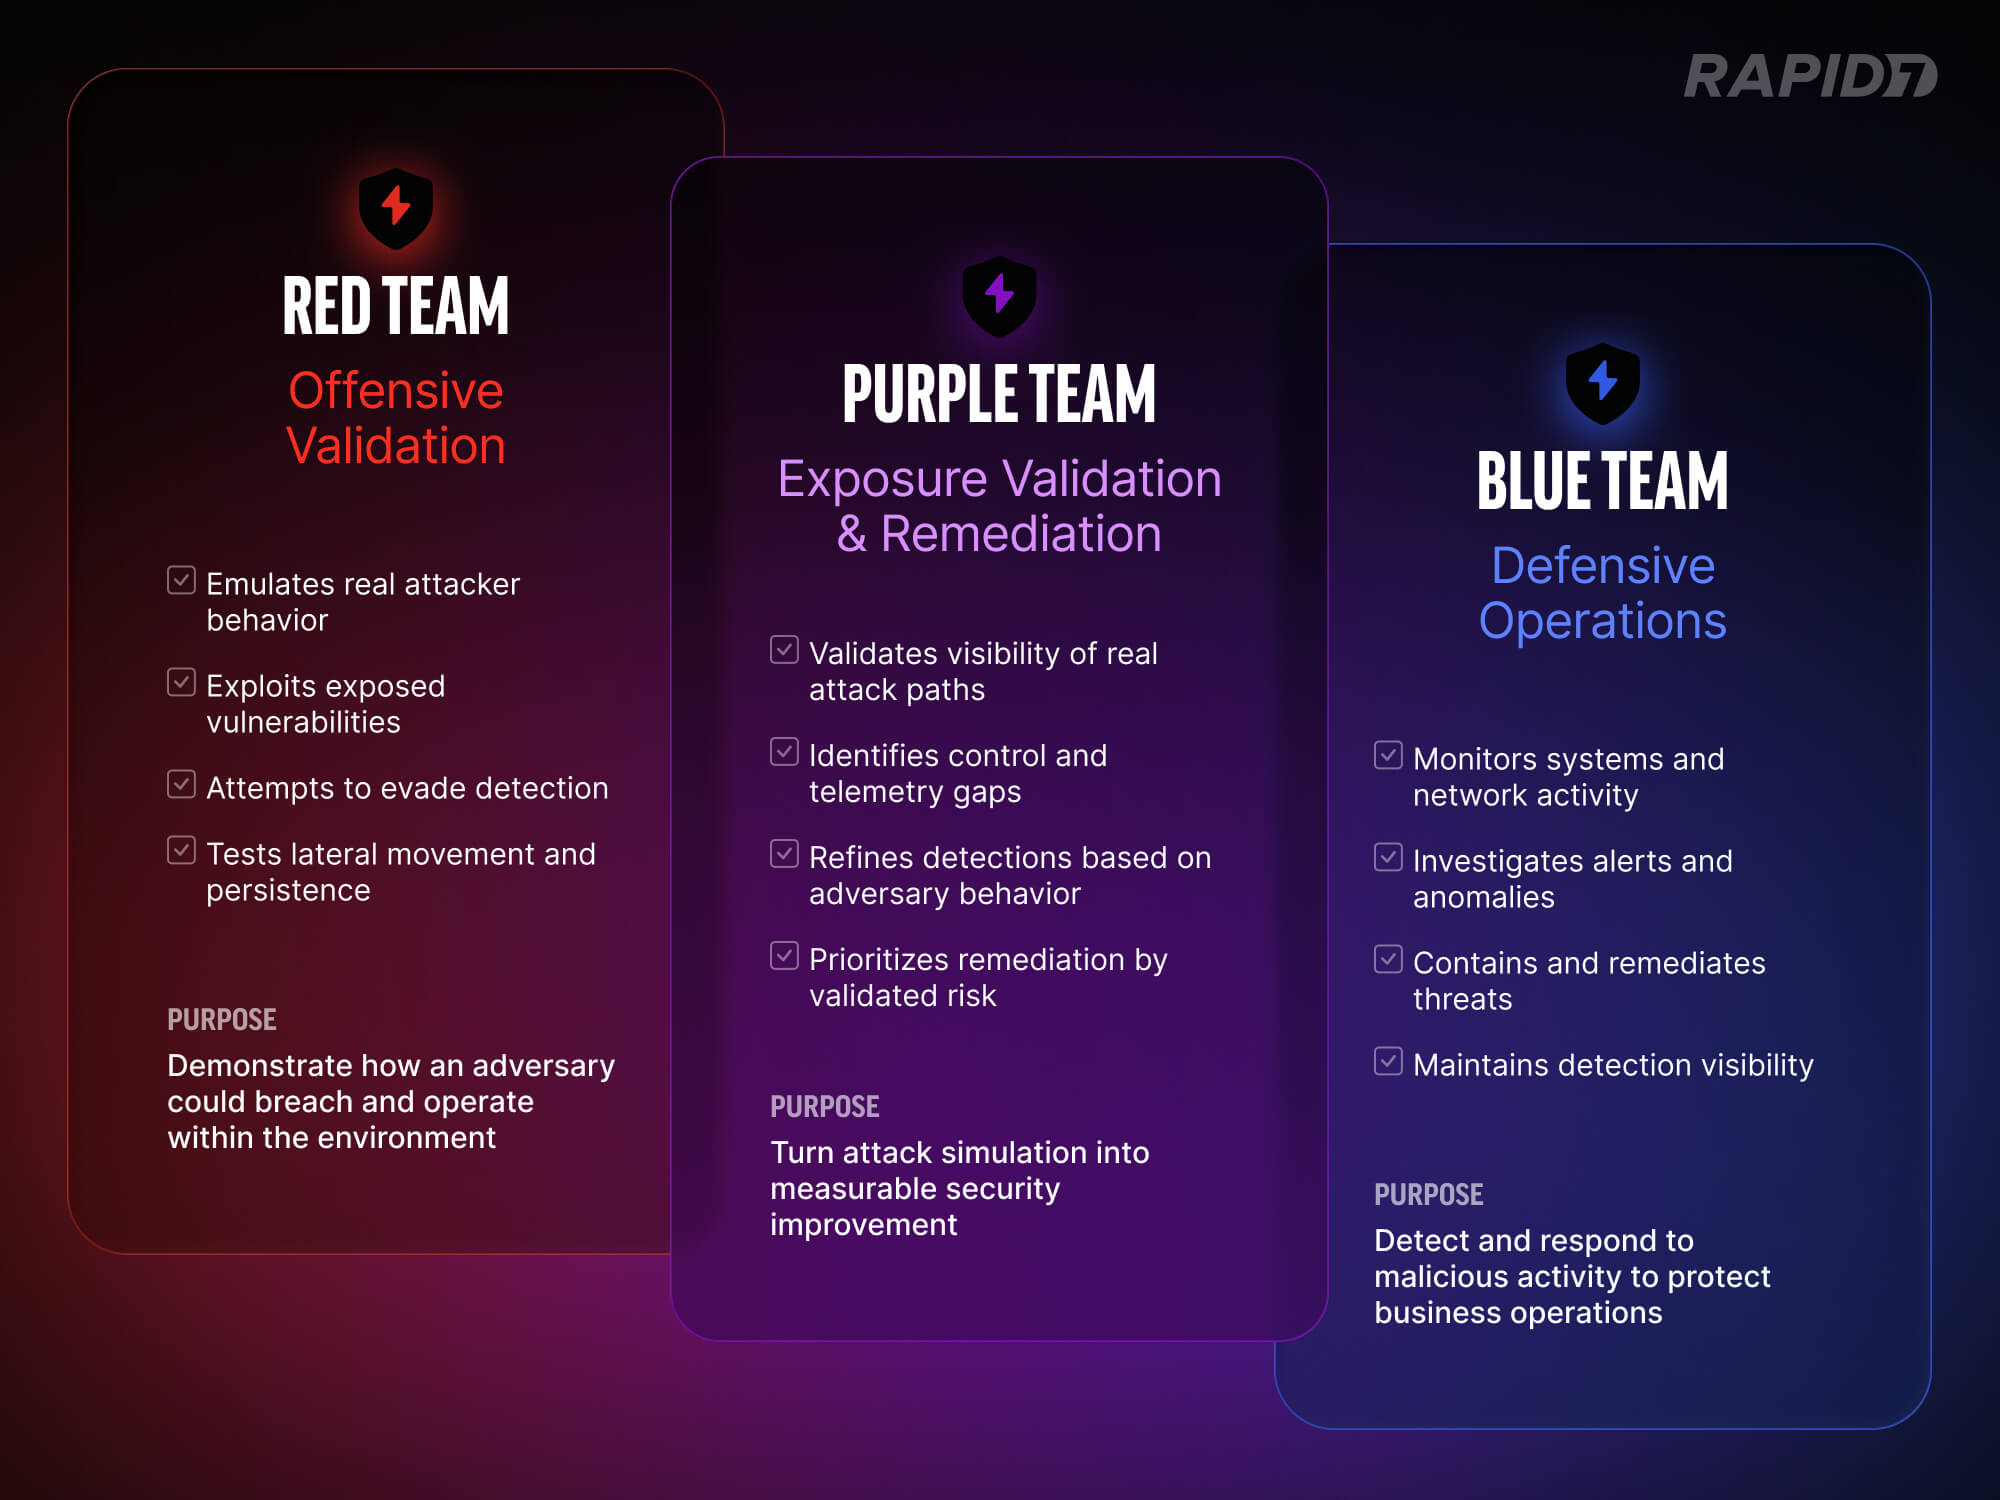
Purple teaming is often described as the collaboration between red teams and blue teams. That definition is accurate, but incomplete. At its core, purple teaming is about exposure validation: deliberately testing whether the threats you believe you can detect and contain are actually visible in your environment.

Red teams simulate attacker behavior. Blue teams defend and respond. Purple teaming ensures those two functions operate in lockstep, sharing telemetry, assumptions, and findings to strengthen detection coverage and close control gaps.

How Red and Blue teams in security combine for Purple Teaming

Unlike traditional penetration testing, which is often point-in-time and compliance-driven, purple teaming is iterative. It is designed to measure, refine, and retest. The goal is not to “win” an exercise. The goal is to improve the organization’s ability to detect, investigate, and contain real attack paths.

Many security programs look mature on paper. Controls are deployed. EDR is in place. Logging is centralized. Dashboards show green indicators. Yet when realistic attacker behavior is exercised inside the environment, gaps often surface quickly. Telemetry may be incomplete. Detection rules may exist but lack tuning. Alerts may trigger without clear ownership or response workflow.

Purple teaming exists to close the gap between perceived protection and actual defensive capability. It replaces assumption with validation.

What purple teaming actually means in 2026

Purple teaming is often described as collaboration between red and blue teams. In practice, it is structured exposure validation conducted in an open-book format.

Offensive operators simulate real-world attack scenarios in coordination with defensive teams. The security operations or incident response team is aware of the exercise from the outset. Together, they define the threat scenarios to test specific response playbooks and detection coverage. The objective is not to surprise the SOC. It is to measure whether detection, telemetry, and response workflows operate as intended and to refine them in real time.

If defensive teams cannot follow a tactic or lack necessary telemetry, activities pause. Gaps are identified and corrected collaboratively. Purple teaming strengthens detection engineering, investigative workflows, and cross-team communication without the pressure of a live incident.

Beyond scorecards: Real-world context matters

Some organizations equate purple teaming with automated breach and attack simulation tools. A sequence of techniques is executed against an assumed compromised host, and a report shows which detection rules are fired. Those metrics can provide visibility into rule coverage. They do not show whether an attacker can exploit real exposures in the environment.

A more contextual approach begins with tailored threat scenarios based on the organization’s actual risk profile. Operators assess real vulnerabilities and misconfigurations rather than firing generic techniques. The focus is not simply to validate rules but to determine whether exploitable exposures exist that blend into legitimate functionality.

Attackers often operate within intended system behavior. They abuse excessive permissions, leverage trust relationships, and exploit architectural weaknesses that were never designed to generate alerts. In these cases, writing a new detection rule does not address the underlying issue. The exposure stems from posture and configuration.

Lateral movement is then executed using access that genuinely exists in the environment. The question becomes whether the organization can observe attacker progression through normal administrative pathways and whether defensive visibility extends beyond initial compromise.

Persistence techniques are established in ways consistent with how an adversary would maintain access in that specific configuration. Detection is measured continuously.

The engagement concludes with a collaborative hunt exercise. The breach lifecycle is recreated without triggering alerts, followed by the intentional generation of a single alert. Teams then work from that signal to reconstruct the attack chain. This phase often reveals how tooling, telemetry, and processes function under structured scrutiny.

Where red teaming fits: Vector Command

It is important to distinguish purple teaming from red teaming.

In a true red team engagement, the SOC and incident response teams are not aware of the breach. Operators attempt to remain undetected for as long as possible. The goal is to emulate a real adversary and test how the organization responds under live conditions.

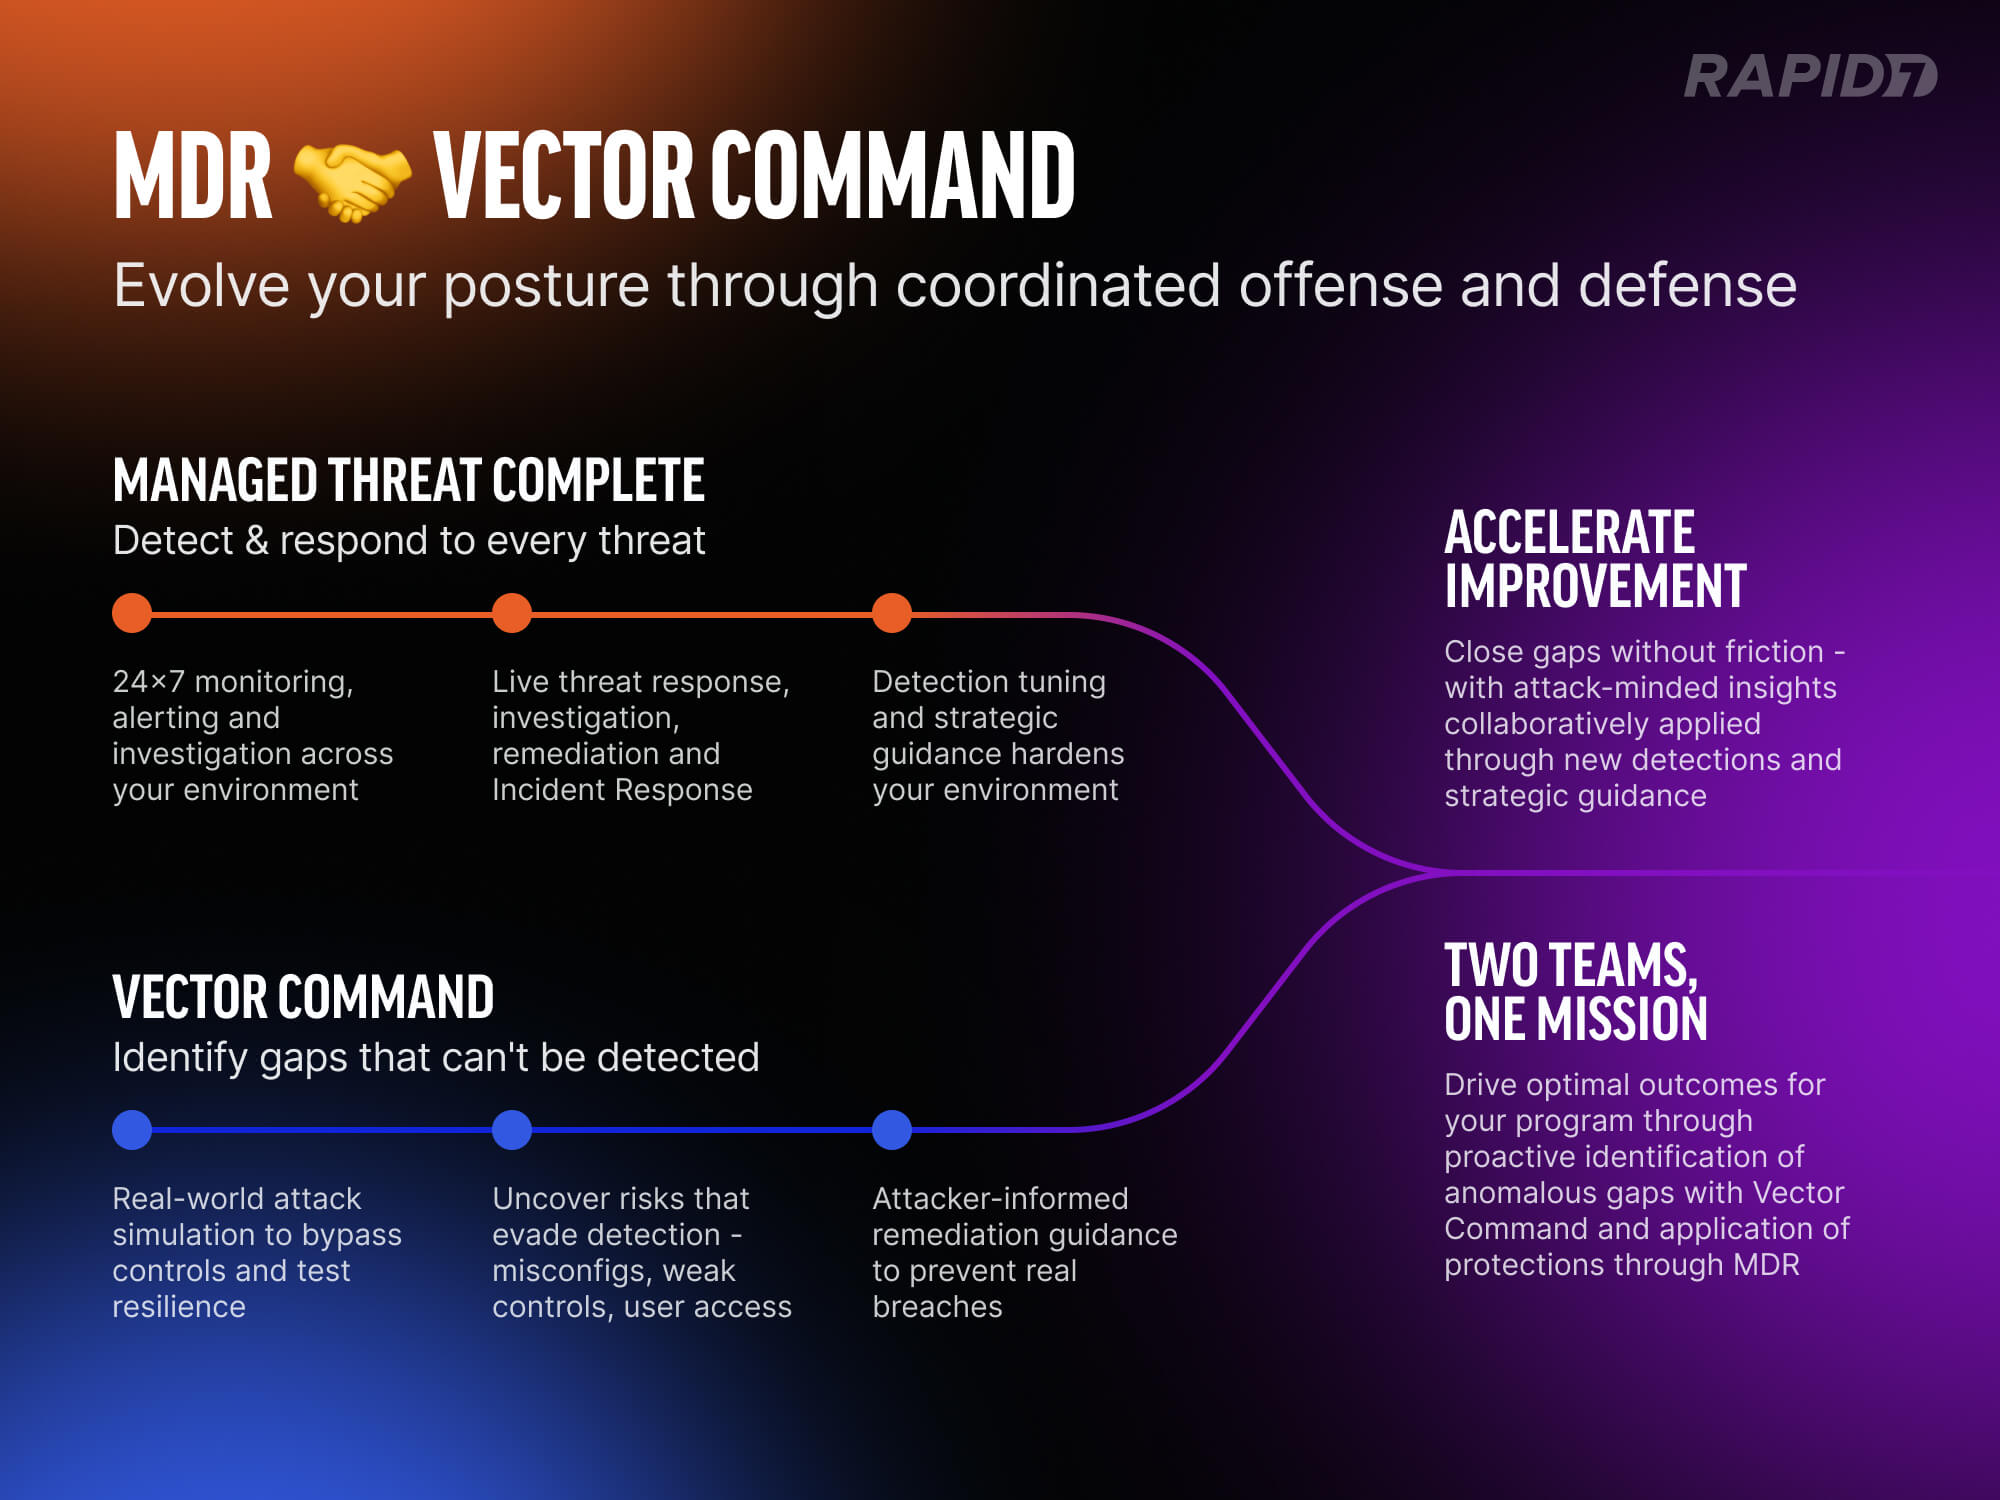
This is how Vector Command operates. It functions as a continuous red team service, attempting to breach client environments and achieve defined objectives while avoiding detection. If detection occurs during a red team engagement, the SOC response is observed as it would be during a genuine incident. This tests process maturity, investigative speed, and real-world visibility. If and when a breach is detected, the engagement can transition into a collaborative purple team phase. At that point, operators work openly with the SOC to walk through the attack path, identify detection gaps, and refine telemetry and response workflows.

Red teaming measures whether defenses hold up under pressure. Purple teaming refines those defenses collaboratively.

The two approaches are complementary. A red team engagement may identify a successful breach path. After that breach concludes, organizations can transition into purple team activities. Offensive findings are shared openly with defensive teams, and gaps are tuned and remediated. When paired with managed detection and response services, this refinement can occur in coordination with both the customer’s security team and the managed SOC.

Purple Teaming via Rapid7's Vector Command

In this model, red teaming exposes real weaknesses. Purple teaming strengthens defenses against them.

What effective purple teaming delivers

Effective purple teaming produces operational improvement rather than a static report.

  • Detection logic improves because it is tuned against real attacker behavior

  • Telemetry gaps are identified and corrected

  • Ownership of investigation workflows becomes clear

  • Remediation is prioritized against validated attack paths rather than theoretical risk

For senior security leaders, the value is measurable control effectiveness. Purple teaming provides evidence that investments in tools and people translate into improved resilience. It also builds alignment between offensive and defensive teams. That alignment accelerates improvement and reduces friction across security, IT, and operations.

In an environment where attack techniques evolve and exposure surfaces expand, purple teaming offers something concrete: validated insight into how well the organization can detect, investigate, and contain adversary behavior.

Resilience should not be assumed. It should be tested.

Threats don’t wait, neither should you: Mastering Emergent Threat Response Validation

Post Syndicated from Ed Montgomery original https://blog.rapid7.com/2025/05/23/mastering-emergent-threat-response-validation/

Cybersecurity is a team sport

Threats don’t wait, neither should you: Mastering Emergent Threat Response Validation

In cybersecurity, no one fights alone. Defending against modern threats requires seamless collaboration, real-time intelligence, and precision execution—just like a well-coordinated sports team. That’s why Rapid7 Labs and our Vector Command team work together to stay ahead of adversaries, ensuring security teams have the insights and capabilities needed to respond effectively. While Rapid7 Labs uncovers emerging threats and delivers cutting-edge research, Vector Command puts that intelligence to work—validating response strategies, optimizing defenses, and ensuring organizations are ready when it matters most. Because in cybersecurity, the best defense is a well-prepared team.

What is an Emergent Threat Response?

Rapid7’s Emergent Threat Response (ETR) program from Rapid7 Labs delivers fast, expert analysis and first-rate security content for the highest-priority security threats to help both Rapid7 customers and the greater security community understand their exposure and act quickly to defend their networks against rising threats.

The Rapid7 Command Platform displays any emergent threats on our homepage, at the top of the screen, easily visible once you have logged in. Our expert researchers include a blog post to accompany each emergent threat.

We also notify all Managed Service customers after discovering new Common Vulnerabilities and Exposures (CVEs). This notification includes known information about the CVE, steps to protect your environment and updates on Rapid7’s response.

Threats don’t wait, neither should you: Mastering Emergent Threat Response Validation
Figure 1: An example of how the Emergent Threat message is displayed on our Command Platform home page
Threats don’t wait, neither should you: Mastering Emergent Threat Response Validation
Figure 2: A close-up view of the actual Emergent Threat message with supporting blog post.

Why is ETR critical?

Emergent threat response validation is critical because cyber threats evolve at a relentless pace, often outpacing traditional security measures. Without continuous testing and refinement, even the most advanced security tools can fall short when faced with real-world attacks. By proactively validating threat response strategies, organizations can identify gaps, fine-tune automation, and ensure that security teams are ready to act with speed and precision. This not only minimizes downtime and damage but also strengthens overall resilience, enabling businesses to stay ahead of adversaries rather than scrambling to react after an incident has already occurred. In today’s threat landscape, preparedness isn’t optional—it’s the difference between containment and catastrophe.

Threats don’t wait, neither should you: Mastering Emergent Threat Response Validation
Figure 3: Emergent Threat Alert message.

How can Vector Command help?

This is the value of an always-on, managed red team service. We continuously test your defenses against the latest ETRs, to see if we can breach your network before threat actors do. If we’re successful, we’ll show you how—and provide actionable remediation guidance.

We’d love to highlight the many organizations that have benefited from this capability with Vector Command, however, we respect their privacy.

One example we can share: a global professional services firm adopted Vector Command for this exact use case. As a frequent target of advanced persistent threats, their security team recognized the value of proactive testing of their resilience.

DORA compliance was also a key driver for this client, given their customer footprint in the EU and the requirement to have reporting. DORA compliance reports demonstrate how financial entities meet regulatory expectations around ICT risk management, incident handling, and third-party oversight—ensuring operational resilience.

With Vector Command, we deliver ongoing external network penetration testing. For some customers, this alone is enough to demonstrate to auditors that they are actively validating their defenses in alignment with DORA.

CTEM and Validation

The leading industry analyst, Gartner®, has said, “security operations managers should go beyond vulnerability management and build a continuous threat exposure management program to more effectively scope and remediate exposures”.

Threat exposure management involves identifying, assessing, and mitigating exposures within an organization’s digital environment. CTEM has emerged as a dynamic program designed to help teams manage their expanding attack surface and maintain a consistent, actionable security posture.

The fourth phase of CTEM is the validation phase and this is where always on red teaming, like Vector Command becomes essential.

Rapid7 also supports the second, third and fifth phases of CTEM through our Exposure Command and Exposure Command Advanced, both launched in August 2024.

Threats don’t wait, neither should you: Mastering Emergent Threat Response Validation
Figure 4: Continuous Threat Exposure Management | Source: Gartner 796532_C

Take command of your attack surface

This is the fourth post in our deep dive blog series exploring key capabilities of Vector Command. We hope you’ve found it valuable—and if you have feedback or questions, we’d love to hear from you.

Rapid7 brings together world-class expertise –  from our Labs researchers and red teamers to the superstars who work across our multiple SOC’s.

If you missed our most recent virtual Take Command 2025 summit, the session, “Outpacing the adversary: Red teaming in a complex threat landscape” is still available on demand. You’ll hear firsthand from industry expert, Will Hunt and Rapid7 principal security consultant, Aaron Herndon.

We’ve also created a self-guided product tour for Vector Command—available anytime for a hands-on look at the platform.

Vector Command: Request Demo ▶︎

Ready to see how continuous red team managed services can ensure your potential attack pathways are remediated before they can ever be exploited?


GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved.

Gartner, “How to Grow Vulnerability Management Into Exposure Management”, November 2024 (For Gartner subscribers only)

Pentales: Red Team vs. N-Day (and How We Won)

Post Syndicated from Ed Montgomery original https://blog.rapid7.com/2025/04/04/pentales-red-team-vs-n-day-and-how-we-won/

Pentales: Red Team vs. N-Day (and How We Won)

During a recent Vector Command operation, I had the chance to sit down with one of our red teamers to hear firsthand how they identified and exploited an N-Day vulnerability in a customer’s environment. It’s a clear example of how continuous red teaming can uncover and validate real-world risks before attackers do.

While the organization involved remains anonymous, the events described are real. This story reflects how our always-on testing approach closely mirrors the creativity and persistence of actual threat actors.

Initial Recon: Spotting an N-Day in the Wild

Vector Command engagements begin with one core question: If someone wanted to break in, where would they start? That’s the mindset our red team brings to every operation.

A red team is a group of security professionals who simulate real-world adversaries. Their goal isn’t to check boxes or run automated scans, but to think and act like attackers—uncovering weaknesses that traditional assessments often miss. They combine technical skill with creativity, adapting to the environment they’re targeting and exploring how far a real compromise could go.

In this case, as part of Vector Command’s continuous reconnaissance, the red team identified a subdomain hosting a vulnerable web application. The vulnerability, already publicly disclosed, classified the exposure as an N-Day. While the issue was known in the broader security community, it hadn’t yet been patched in this environment.

Using a publicly available proof-of-concept exploit, the team compromised the application and underlying host. From there, they found credentials stored in the file system, granting access to services deeper within the internal network.

From Exploit to Expansion: Breaching the Perimeter and Moving Laterally

As part of our recon, we zeroed in on a subdomain running a web app that was just begging to be poked. It was tied to a recently disclosed N-Day vulnerability—publicly known, actively discussed, and in this case, still unpatched.

We ran a proof-of-concept exploit and landed a shell. From there, we had access to the underlying host, and it didn’t take long to find something useful: credentials stashed away on the file system. Those creds gave us our next step into the internal network.

With the perimeter breached, we started exploring. There was little in the way of segmentation, which made internal discovery a breeze. We quickly found an internal SMTP server and realized we could send emails that appeared completely legit—from the inside, to the inside.

We used that to spin up a phishing campaign. The bait? A cloned version of the company’s actual login portal, hosted on the compromised subdomain. From the user’s perspective, everything looked familiar. The URL checked out. The branding was perfect. And people clicked.

We captured multiple sets of credentials, including an admin account. From there, we confirmed a misconfiguration on a critical internal system. That allowed us to escalate privileges and prepare for full domain takeover.

Classic attack chain: exploit, phish, pivot, escalate. All real. All tested safely under Vector Command.

From Attack Chain to Action Plan

You may be forgiven for thinking an organization would not be happy with this. However, it is exactly the opposite and our Vector Command customer was delighted we found and exploited this vulnerability. We proved the value of our continuous red teaming, mimicking what a real external threat actor would do to breach a network.

The sub-domain we compromised was prioritized for remediation and now has security controls in place. We then re-tested the customer’s environment to ensure their patches actually worked and this particular security gap was closed.

From PoC’s to Happy SOC’s

In our previous blogs, we’ve explored the human side of continuous red teaming—through opportunistic phishing stories, external network assessments, and a deep dive into the TTPs behind post-compromise simulations.

Security Operations Centers (SOCs) are often relieved—not rattled—when we uncover these risks. It gives them proof, insight, and time to act.

As part of Vector Command, this engagement was fully documented—summarized for executive stakeholders and detailed for security practitioners. Reports live in the Vector Command portal, accessible whenever teams need to revisit findings or track remediation progress.

Customers also have the opportunity to debrief directly with the red teamer behind the operation. Whether it’s to dig deeper into the attack chain or walk through lessons learned, we’re here to help strengthen defenses—because at the end of the day, we’re all working toward the same goal.

If you or your security team want to explore how continuous red teaming can support your program, let’s talk.

Ready for Your Own Red Team Reality Check?

If you’re curious what an attacker might find in your environment, Vector Command can help you find out before someone else does.

Learn More about Rapid7’s Vector Command Service ▶︎

Ready to see how continuous red team managed services can ensure your potential attack pathways are remediated before they can ever be exploited?

Unpacking a post-compromise breach simulation with Vector Command

Post Syndicated from Ed Montgomery original https://blog.rapid7.com/2025/03/27/unpacking-a-post-compromise-breach-simulation-with-vector-command/

The reality of modern cyber threats

Unpacking a post-compromise breach simulation with Vector Command

In today’s evolving cyber landscape, breaches are not a matter of if, but when. Attackers continue to refine their techniques, using stealthy post-compromise tactics to maintain persistence, escalate privileges, and move laterally across networks. The key to staying ahead is not just preventing attacks, but building resilience to withstand and respond to them effectively.

This concept of resilience aligns with Continuous Threat Exposure Management (CTEM), a proactive approach to security validation. According to Gartner, CTEM consists of five pillars:

When we look at the five pillars, described by Gartner:

  1. Scope of your organization’s attack surface;
  2. Discover your attack surface;
  3. Prioritize your vulnerabilities;
  4. Validate security controls and finally;
  5. Mobilize people and processes to operationalize the CTEM findings.

Vector Command plays a critical role in the fourth pillar, continuously testing security defenses through post-compromise breach simulations that replicate real-world adversary tactics.

How Vector Command tests resilience

This blog is the third in our Vector Command series, where we explore the tactics, techniques, and procedures (TTPs) leveraged by Rapid7’s expert red team. Today, we’re focusing on post-compromise breach simulations—a critical capability in assessing an organization’s ability to detect and respond to a persistent adversary.

Unpacking a post-compromise breach simulation with Vector Command
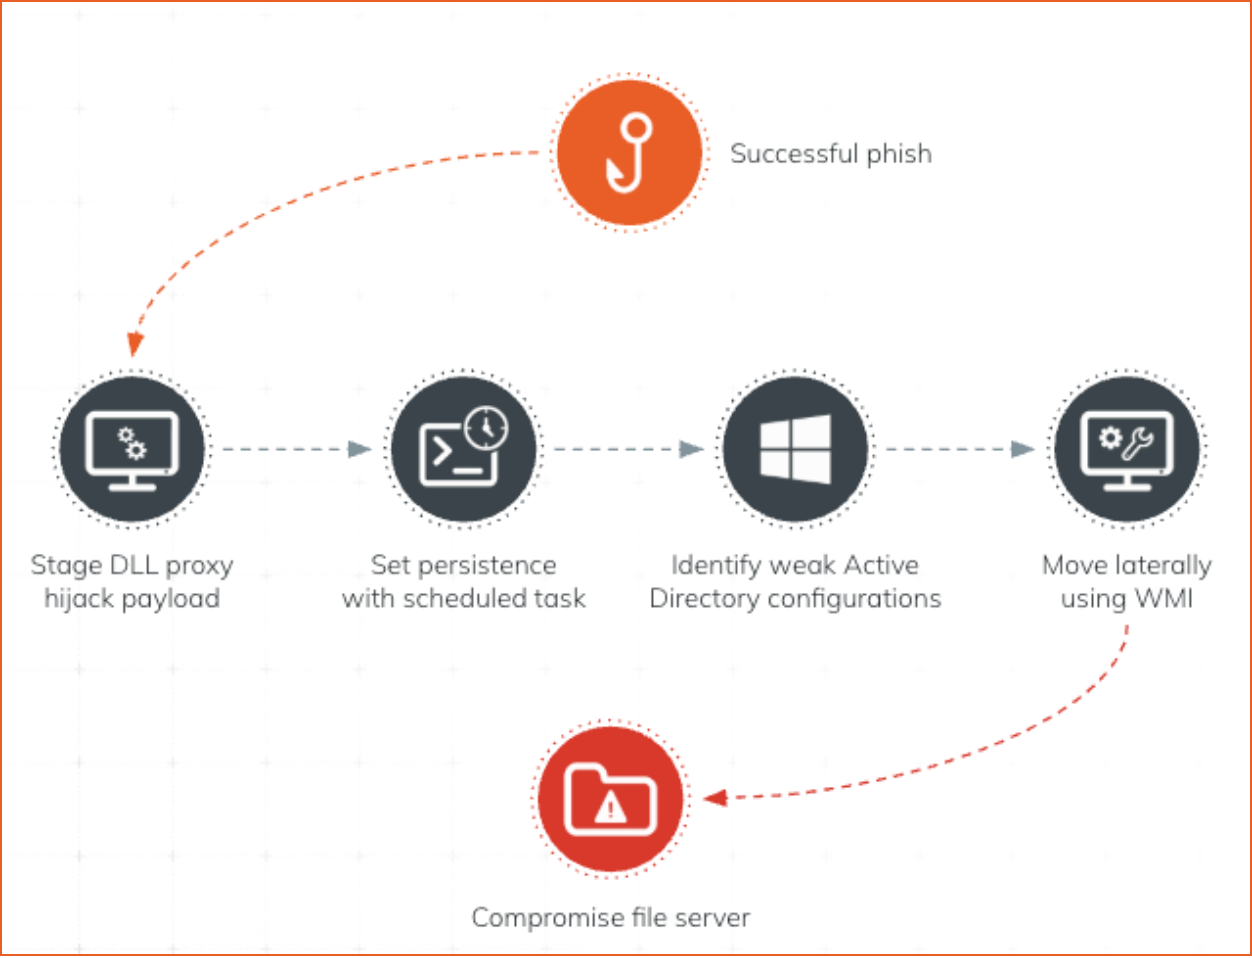
Figure 1: Post Compromise Breach Simulation Attack

TTP mapping to the MITRE ATT&CK framework

Once an attacker gains access—whether through phishing or external exploitation—the real damage begins. As part of our post-compromise breach simulation, Vector Command emulates the tactics and techniques adversaries use once they’re inside, leveraging the MITRE ATT&CK® frameworks as a guide.

Our red team stages command and control payloads and executes a series of proven attacker behaviors to test your resilience across the most common post-compromise scenarios:

  • Configure host persistence – Attackers work to maintain their foothold across reboots and user sessions by modifying startup tasks, hijacking processes, or introducing malicious code. We simulate these tactics to test your defenses against long-term compromise.
  • Attempt host privilege escalation – Gaining initial access is just the beginning. Adversaries often exploit misconfigurations or unpatched vulnerabilities to escalate privileges from standard user accounts to full admin control—enabling deeper access into your environment.
  • Query Active Directory for hosts accessible with compromised credentials – With valid credentials in hand—often obtained through phishing—we test whether an attacker could identify and access other systems or sensitive services using tools that mimic common enumeration techniques.
  • Attempt lateral movement on the network – We simulate how attackers move through your environment by pivoting between systems using native tools and compromised credentials. This reveals how far a real threat actor could go—and how quickly they’d reach your most critical assets.
  • Attempt domain privilege escalation using common misconfigurations – During breach simulations, our red team frequently tests for domain privilege escalation using misconfigurations that are surprisingly common in real-world environments. These include:
  • Local administrator accounts
  • Users with admin-like access
  • Standard users with elevated access to specific systems or sensitive functions

These misconfigurations often intersect with persistence techniques, as attackers take advantage of elevated contexts to maintain long-term access.

Want to see how exposed your organization might be? Surface Command can help identify admin users without multi-factor authentication (MFA), offering a quick view into high-risk accounts and helping fulfill the “Discover” step of Exposure Management.(See our Surface Command Admin users without MFA use case

  • Initial access payloads and internal breach playbooksEvery simulation is guided by detailed internal breach playbooks. These help test your incident response readiness and ensure alignment with known attacker workflows, including phishing payload delivery and post-access exploitation.

Each of these steps represents a real-world risk. By simulating them in a controlled environment, Vector Command helps organizations identify blind spots, validate security controls, and improve detection and response capabilities.

Beyond simulation: Actionable reporting & remediation with Vector Command

Security testing is only as valuable as the insights it delivers. With Vector Command, organizations receive tailored reports designed for both executive leadership and security practitioners:

  • Executive-Level Report: A high-level summary of key findings, business risks, and prioritized remediation steps, written in plain language for strategic decision-making.
  • Technical Report: A detailed breakdown of attack simulations, including timestamps, screenshots, and step-by-step execution logs for the security team to analyze and act on.

These insights are not just reports—they are action plans to help teams fortify their defenses against real adversary behaviors.

Take command of your attack surface

Cyber resilience is about understanding your adversary’s tactics before they use them against you. Vector Command delivers an always-on red teaming service that helps organizations stay ahead of attackers by continuously validating defenses and improving response strategies.

Want to learn more? Join us at our upcoming Take Command virtual summit, where we’ll explore how red teaming is evolving to outpace modern threats.

Register here.

Explaining External Network Assessment with Vector Command

Post Syndicated from Ed Montgomery original https://blog.rapid7.com/2025/03/12/explaining-external-network-assessment-with-vector-command/

Explaining External Network Assessment with Vector Command

Learn how external network assessment works within Vector Command, Rapid7’s continuous red team managed service.

Understanding threat exposure management

Let’s start by providing some context around where Vector Command fits into a security program and more specifically Continuous Threat Exposure Management (CTEM). Threat exposure management involves identifying, assessing, and mitigating exposures within an organization’s digital environment CTEM has emerged as a dynamic program designed to address this expanding footprint and help organizations achieve a consistent and actionable security posture.

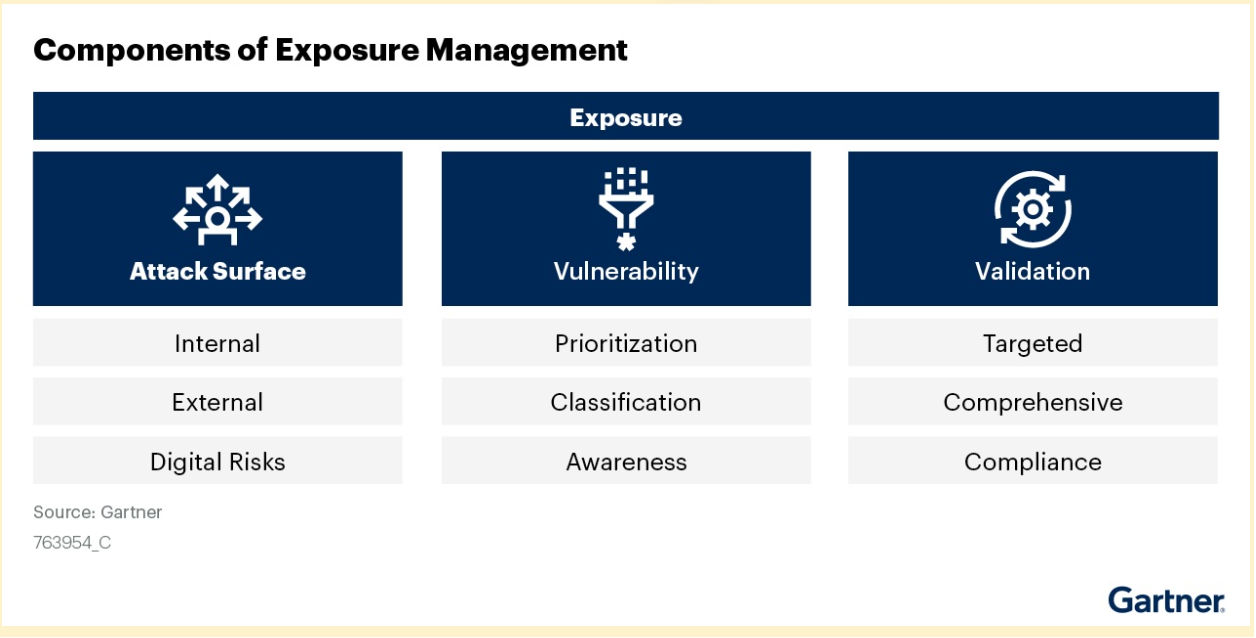
According to Gartner, some of the different technologies that can support a wider CTEM program can be organized into three distinct pillars:

Explaining External Network Assessment with Vector Command

“Your ‘always on’ red team”

Vector Command sits within the validation pillar, your ‘always on’ red team – validating results from technologies or services as well as validating that the controls in place are working as anticipated.

Explaining an external network assessment

An “external network assessment” refers to evaluating the security posture of an organization’s publicly accessible network perimeter. This essentially simulates a hacker’s perspective to identify vulnerabilities on systems and services directly reachable from the internet. This will include web servers, email servers, and exposed ports, to assess potential risks and weaknesses that could be exploited by malicious actors.

Goals of an external network assessment:

  • Our red team is looking to discover potential entry points for attackers.
  • Identify misconfigurations and weak security practices on exposed systems.
  • Evaluate the overall security posture of the external network perimeter.

Rapid7’s Vector Command red team testing approach

Our Vector Command red team experts conduct comprehensive security assessments using a multi-faceted approach:

Initial discovery and assessment

We begin by leveraging EASM-discovered assets and IVM scan results to map your approved attack surface. Our experts validate IVM findings and conduct service discovery to ensure complete coverage.

Vulnerability identification

Our team searches for common web misconfigurations through directory testing, reviews exposed administrative functions, and checks for unauthenticated access to sensitive areas. We also conduct limited, non-intrusive password testing against services like email, IAM, and VPNs using information gathered during EASM scanning.

Continuous monitoring and testing

As an always-on managed service, we:

  • Perform vulnerability scans using InsightVM
  • Validate potentially exploitable findings before publishing them to your portal
  • Monitor Rapid7’s Emergent Threat Response channels for new critical vulnerabilities
  • Evaluate and test public Proof of Concept exploits when applicable
  • Execute payloads to demonstrate successful breaches
  • Assess credentials obtained through phishing campaigns
  • Continuously retest your environment to ensure ongoing security

Throughout this process, we build comprehensive documentation of your attack landscape to inform future security assessments.

Take command of your attack surface

Rapid7 strengthens your organization’s security strategy through Vector Command, delivering comprehensive CTEM alongside our other exposure management solutions.

With Vector Command, customers can now have a team of experts continuously assess their external attack surface. This includes identifying any security gaps, and receiving remediation guidance on an ongoing basis.

Our series of Vector Command blog posts will continue and next up we will cover the TTP Post-Compromise Breach Simulation.

If you would like to hear more about the world of red teaming from one of our experts behind Vector Command, Rapid7 is running a virtual session at our 2025 Take Command Summit, find out more about it here.

Vector Command Opportunistic Phishing Blog

Post Syndicated from Ed Montgomery original https://blog.rapid7.com/2025/02/07/vector-command-opportunistic-phishing-blog/

Gone Phishing with Vector Command

Vector Command Opportunistic Phishing Blog

During one of our customer engagements, our red team will continuously attack your network to see if we can exploit a vulnerability. One of the tactics, techniques and procedures (TTPs) we use is “Opportunistic Phishing”. First, let’s share a quick reminder about what Vector Command is.

Vector Command is Rapid7’s new continuous red teaming managed service, designed to  assess your external attack surface and identify gaps in the security defenses on an ongoing basis. Vector Command continues the expansion of our Exposure Management solutions for our customers. While external attack surface management (EASM) tools offer visibility, they often fall short in validation, generating lengthy lists of potential exposures for security teams to sift through. Traditional penetration testing can help validate vulnerabilities, but its point-in-time nature risks leaving critical exposures undetected for extended periods. With Vector Command, our red team will continuously look for exploitable vulnerabilities.

Vector Command Opportunistic Phishing Blog
Rapid7’s Vector Command Landing page

Hacking the Human

Social engineering attacks are based on the exploitation of someone’s personality and can be referred to as “hacking the human”.

Security professionals often comment how the employee can often be the weakest link in a company’s security posture. From end-of-day tiredness, to our more relaxed nature during a quick lunch break and even our predisposed trusting tendencies towards those causes we care deeply about, can be exploited by threat actors. This is the “social” aspect in “Social Engineering”. Humans can be manipulated into making mistakes through psychological means and giving our login credentials away or other sensitive information.

Opportunistic Phishing – The Human Touch

Opportunistic Phishing, also known as “untargeted attacks” may have no warning signs and is often deployed spontaneously, without a specific target. Rapid7’s red team will use this technique to see what information they can get from a customer engagement.

Let’s take the hypothetical example of a former IT contractor who was employed by a company. The off-boarding policy has not yet been completed. The IT contractor had elevated access to one business application containing personally identifiable information (PII). Our red team, once they identify this former contracted employee, could use their access rights to gain entry to sensitive PII and services on the corporate network.

When an opportunistic attempt is executed by a threat actor, it is most commonly conducted via malware or phishing over email.

In this specific technique, an attacker will send out fraudulent messages, taking care to design the emails to look like the actual organization, often using similar logos, fonts, and signatures. Inside the body of the message will be a URL, typically with a misspelled domain name or extra subdomain. If the recipient is not savvy enough to recognise the fake web address from the real one and clicks on the link, this is when the malware is activated as an executable file and downloaded to the device. The payload often  includes keylogging software, used to collect keystrokes, including your passwords, which now gives the threat actor access to your company network.

By deploying this tactic, Rapid7’s red team, think, act and behave like a threat actor, but without the malicious consequences for your organization. Using opportunistic phishing, we will find and identify where your security gaps are, with respect to technology (through different configuration types for campaigns) and people, helping you to act and respond. Our advanced Vector Command reporting even gives a detailed outline of the situation, including remediation recommendations for your IT and Security teams.

Vector Command Opportunistic Phishing Blog
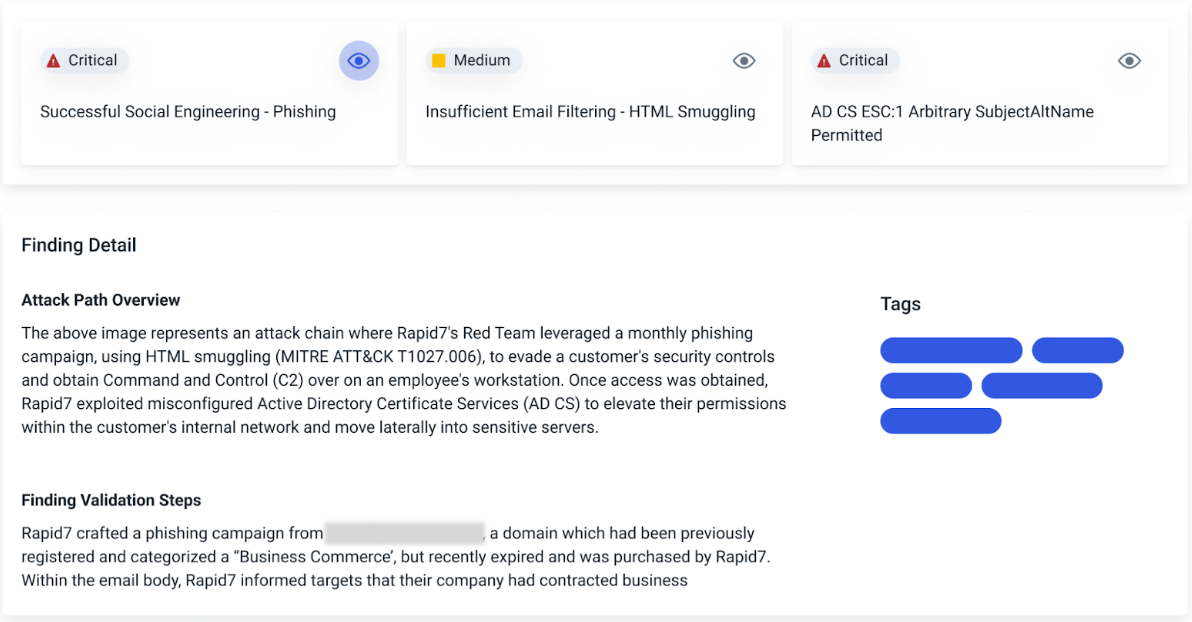
A sample report for a Phishing campaign completed by our Vector Command red team

What should you be on the lookout for?

Let’s explore some typical phishing examples that frequently target organizations.

  • Invoices for companies that you do not have a supplier agreement with.
  • Shipping notifications from large retailers, both online and the high street.
  • Password reset requests for your email, or other online account e.g. Amazon, or PayPal.
  • Tax refund emails either at the time of needing to submit your tax return (when it is time sensitive) or months away from when it needs to be completed (anomalous behavior).
  • Can you spot poor grammar, or spelling errors in the subject, or within the body of the email, that would indicate it is not from a reputable source?
  • Does the email have a sense of urgency – “Act now”?
  • Generic greetings like “Dear Customer” as opposed to a more personalized one.
  • Surveys from third-parties or workplace experience coordinators that are out-of-place.
  • Suspicious login alerts from common applications sourcing from an untrusted sender.
  • Password reset requests for your email, or other online account e.g. Amazon, or PayPal.
  • Employee benefit emails either at the time of needing to submit your elections (when it is time sensitive) or months away from when it needs to be completed (anomalous behavior).
  • Shared documents and calendar invitations from third-parties you do not commonly interact with.
  • Browser extensions, software updates, and installation requests via email or phone.
  • Verify unexpected phone calls through internal communication applications such as Teams, or Slack.

Take Command of your Attack Surface

Stay tuned as we continue to share insights of other TTPs employed by Rapid7’s expert  red team to test your cyber resilience.

We have created a self-guided product tour for Vector Command which you can check out at your leisure.

Vector Command: Request Demo ▶︎

Ready to see how continuous red team managed services can ensure your potential attack pathways are remediated before they can ever be exploited?

Rapid7 Introduces Vector Command, a New Managed Service for Continuous Red Teaming

Post Syndicated from Ed Montgomery original https://blog.rapid7.com/2024/09/17/rapid7-introduces-vector-command-a-new-managed-service-for-continuous-red-teaming/

Rapid7 Introduces Vector Command, a New Managed Service for Continuous Red Teaming

Rapid7 is delighted to announce the launch of Vector Command, a continuous red teaming managed service designed to assess your external attack surface and identify gaps in the security defenses on an ongoing basis. Following the launch of Surface Command and Exposure Command in August, Vector Command will continue our expansion of Exposure Management protection for our customers.

In today’s digital landscape, organizations are more exposed to cyber threats than ever before. Cloud resources, SaaS solutions, and ever-growing shadow IT create vast external attack surfaces, making businesses increasingly vulnerable. Meanwhile attackers are constantly on the prowl, conducting reconnaissance to exploit weaknesses. Security teams lack visibility into their internet-facing exposures, leaving them vulnerable to potential breaches.

While external attack surface management (EASM) tools offer visibility, they often fall short in validation, resulting in lengthy lists of potential exposures for security teams to sift through. Traditional penetration testing can help validate vulnerabilities, but its point-in-time nature risks leaving critical exposures undetected for extended periods.

Introducing Vector Command

Vector Command is designed to address these challenges head-on, providing a continuous, proactive approach to securing your external attack surface by combining Rapid7’s trusted technology for external attack surface assessments with our world-class red team expertise. By providing an attacker’s perspective, Vector Command empowers security teams to visualize internet-facing assets, validate critical exposures, and take decisive action to mitigate risks.

Vector Command benefits include:

  • Increased visibility of the external attack surface with persistent, proactive reconnaissance of both known and unknown internet-facing assets
  • Improved prioritization with ongoing, expert-led red team operations to continuously validate your most critical external exposures
  • Same-day reporting of successful exploits with expert-vetted attack paths for multi-vector attack chains and a curated list of “attractive assets” that are likely to be exploited
  • Monthly expert consultation to confidently drive remediation efforts and resiliency planning

Rapid7 advantage: trusted technology and red team expertise

At the heart of Vector Command is our red team operators, among the best in the industry, bringing years of experience in simulating real-world attacks and identifying vulnerabilities that automated tools might miss. This combined with our recently launched Command Platform’s external attack surface assessment capability provides a unique and powerful solution to ensure that you are not just receiving a list of potential vulnerabilities, but actionable insights based on real-world attack scenarios.

External attack surface assessment: Powered by Rapid7’s Command Platform, Vector Command will leverage the external attack surface capability to perform ongoing, active reconnaissance and discovery of your external attack surface to help you

  • Find the unknown and ensure continuous understanding of where shadow IT or unknown business assets may exist like exposed web services, remote admin services, and more
  • Zero-in on potential remote access risks, and risky or unencrypted services
Rapid7 Introduces Vector Command, a New Managed Service for Continuous Red Teaming

Red team expertise: Our expert operators leverage the latest tactics, techniques, and procedures (TTPs) to safely exploit the external exposures and test your security controls with red team exercises like:

  • Opportunistic phishing – Our experts will design and conduct phishing campaigns using the latest TTPs with focus on demonstrating the impact of credential capture and payload execution.
  • External network assessment – Ongoing assessment of vulnerabilities exposed in the external network, focused on obtaining access to your organization and its sensitive systems.
  • Post-compromise breach simulation – Upon breach, our experts will safely emulate the latest tactics to obtain command and control over the compromised system. Post-exploitation activities emulate adversary behavior to assess privilege escalation, lateral movement, and persistence.
  • Emergent threat validation – Assess your network perimeter’s susceptibility to the latest Rapid7 emergent threat vulnerabilities to validate patching and security configurations.
Rapid7 Introduces Vector Command, a New Managed Service for Continuous Red Teaming

Take command of your attack surface defenses

In an era where cyber threats are constantly evolving, Vector Command empowers you to stay one step ahead of attackers. By providing continuous visibility, validation, and expert guidance, we help you transform your cybersecurity posture from reactive to proactive.

Don’t wait for a breach to expose weaknesses in your defenses. With Vector Command, you can command your attack surface with confidence, knowing that you have Rapid7’s trusted technology and Red Team expertise on your side.

Learn More