You can’t patch everything. So what do you fix first? Findings in Q2 2026 have changed traditional answers.
The latest Quarterly Threat Landscape Report from Rapid7 Labs shows vulnerability disclosures still surging while attackers use automation and AI-assisted tooling to compress the time between disclosure and exploitation. The gap that patch cycles were built to fill is closing. Speed and volume are overwhelming security teams that have relied on traditional patch cycles and reactive programs. Success going forward can’t be about patching as much as possible – it has to be about understanding what matters most and reducing the exposures attackers can actually reach.
Here are the four trends that defined Q2 2026, and what they mean for your security program as you define priorities for Q3 and beyond:
The volume of disclosures hit another milestone
There were 8,539 new high- and critical-severity CVEs (CVSS 7.0–10.0) this quarter- double the number reported in the same quarter last year (4,268). Meanwhile, the number of newly exploited vulnerabilities held roughly steady (40). The takeaway isn’t that exploitation exploded – it’s that disclosure volume is far outstripping what any team can triage.
The report breaks down which of those disclosures are actually reachable and how to triage by exploitability instead of severity score alone.
Initial access keeps getting easier
Nearly two-thirds of exploited vulnerabilities this quarter (62%) required no user interaction – no stolen credentials, no phishing victim, no click. Attackers reach and exploit them on their own, and that share is up nine points year over year (from 53% in Q2 2025). Reinforcing the trend, disclosures of missing-authentication flaws (CWE-306) surged 247% year over year – a fast-expanding pool of internet-facing systems that require no login at all.
This is the quarter’s clearest signal – and the report details exactly which exposures to close first, and how, before the exploitation curve catches up.
Nation-state activity remains persistent
Rapid7 observed continued activity from Iranian, North Korean, and Russian advanced persistent threat (APT) clusters targeting government, finance, healthcare, manufacturing, energy, and telecommunications. Russian campaigns targeted edge infrastructure; Iranian activity included sustained industrial control system (ICS) and operational technology (OT) targeting.
The report maps the specific techniques and sectors each cluster focused on this quarter.
Ransomware stays concentrated but keeps evolving
Qilin led ransomware activity in Q2 with 263 listed victims, and the United States remained the most heavily targeted country – with business services and healthcare among the hardest-hit sectors. Rapid7’s Incident Response team also saw growing use of ClickFix and fake CAPTCHA campaigns, and social engineering through trusted collaboration platforms like Microsoft Teams – techniques that accounted for 31.8% of the incidents we worked.
The report includes the full ransomware leaderboard, the sectors most at risk, and where affiliate activity is expanding next.
Exposure is the real challenge, and the biggest opportunity
The volume is daunting, but the real challenge is keeping pace with attackers. As disclosures keep growing, the organizations that stay ahead won’t be the ones patching fastest — they’ll be the ones that know what they expose, which assets matter most, where attackers can realistically get in, and how to reduce reachable exposure before it becomes an incident. That’s what preemptive security means: not a slogan, but an operating model.
The full Quarterly Threat Landscape Report shows where reachable exposure concentrates this quarter, the four actions Rapid7 Labs recommends, the sector-by-sector breakdown, and the dark-web signals shaping what’s next. Read it here before you pressure-test your Q3 prioritization.
The first quarter of 2026 reinforced that attackers are moving faster, operating with greater coordination, and exploiting weaknesses before most organizations can respond effectively. From escalating geopolitical tensions to increasingly aggressive ransomware operations, the latest quarterly Threat Landscape Report highlights a security environment where reactive defense strategies are becoming unsustainable.
Quarterly Threat Landscape Report findings
Exploits unseat social engineering for top initial access vector (IAV)
One of the biggest takeaways is that vulnerability exploitation surpassed social engineering as the largest initial access vector with 38% of the total. This would be interesting on its own, but when coupled with more than 50% of all exploited vulnerabilities actively being zero-click, network facing vulnerabilities, it indicates that, at least in the short term, attackers are finding AI-enabled vulnerability exploitation easier to accomplish than exploiting human behavior. These types of vulnerabilities require no authentication and no user interaction, giving attackers rapid pathways into exposed systems and edge infrastructure. At the same time, exploitation activity was frequently preceded by large spikes in public discussion across forums, blogs, and social media platforms, demonstrating how quickly threat actors operationalize publicly available information once vulnerabilities gain visibility.
Geopolitics and FBI takedowns in the threat landscape
Geopolitical instability also continued to shape cyber operations throughout the quarter, particularly in the Middle East, where cyber activity was increasingly synchronized with military escalation. Iranian state-aligned groups targeted government infrastructure, financial services, and industrial systems, while Russian and Chinese campaigns focused heavily on intelligence collection, telecommunications infrastructure, and persistent access operations designed to remain undetected over long periods of time. The result is a threat landscape where organizations must prepare not only for immediate disruption, but also for long-term persistence inside enterprise environments.
Meanwhile, law enforcement operations targeting underground criminal infrastructure disrupted several major ransomware and credential marketplaces during Q1, including the seizure of RAMP and LeakBase. These takedowns have created operational pressure for cybercriminal groups, pushing threat actors toward smaller, decentralized communities and increasing internal distrust.
A marked shift towards “pure extortion”
The report also highlights the continued evolution of ransomware operations, particularly the growing shift toward “pure extortion” tactics focused on rapid data theft rather than traditional encryption-based attacks. Threat actors increasingly leveraged zero-click vulnerabilities to gain initial access, exfiltrate sensitive data, and pressure victims without deploying ransomware payloads that create additional operational risk and visibility.
Taken together, the findings from Q1 2026 show that organizations can no longer rely on periodic assessments and reactive workflows alone. Security teams need continuous visibility into their attack surface, better prioritization around exploitable risk, and the ability to move at a pace that matches modern attackers before small exposures become large-scale incidents.
Ransomware and other disruptive attacks rarely succeed because of a single catastrophic failure. More often, they succeed because a system was designed for availability and scale, but not for persistent, adaptive adversaries testing for weak points from the outside.
For infrastructure and architecture leaders, that creates a practical challenge: how do you build systems that remain performant, cost-efficient, and operable while also standing up to attackers who are probing your environment for opportunities through traffic abuse, credential attacks, vulnerability exploitation, and social engineering?
The answer is not a single tool or framework. It is an architectural mindset: assume adversaries exist, assume controls will be tested, and design systems that continue operating safely under pressure.
Security starts with architecture, not alerts
One of the most common mistakes organizations make is treating security as something layered onto infrastructure after it is built. In practice, resilience comes from decisions made much earlier:
How traffic is handled under stress.
How systems and services are segmented.
How identity and access are enforced.
How quickly vulnerabilities are surfaced and validated.
How failure is contained when something goes wrong.
This is what separates reactive security from resilient architecture. The strongest environments are not the ones with the most dashboards; they are the ones built so that no single weakness can easily cascade into a broader incident.
Designing the perimeter to buy time, not perfection
Even in a world shaped by zero trust, the perimeter still matters, especially for availability.
Large-scale traffic floods, automated scanning, and API abuse are often the opening move. These events may not be the full attack, but they can create noise, consume resources, and open the door for more targeted follow-on activity. Infrastructure teams need defenses that can:
Absorb unexpected traffic without cascading failures
Distinguish abusive patterns from legitimate use
Prevent noisy attacks from turning into operational incidents
These defenses can never provide perfect prevention; cybercriminals can attack with too much sophistication and velocity. Rather, the goal is resilience. Good perimeter design buys time, preserves service availability, and prevents external pressure from becoming internal disruption.
Modern environments change too quickly for occasional reviews to be enough.
Attackers do not work on quarterly schedules, and neither should defensive programs. A stronger model is continuous vulnerability discovery: using multiple signals to understand what is exposed, what is exploitable, and what actually matters.
That can include a mix of:
Threat intelligence on active exploitation trends
External research programs such as bug bounties
Regular penetration testing
Internal testing and automated vulnerability scanning
Each of these presents different types of risk. Together, they reduce blind spots and help teams prioritize fixes based on real-world likelihood and impact, not just severity scores on paper.
Limiting blast radius is an architectural responsibility
A useful security question is not only “How do we stop every attack?” but also “What happens if one control fails?”
That shift changes how teams think about system design. It places greater emphasis on:
Hardening critical systems
Enforcing strict access controls
Separating environments and services
Reducing unnecessary trust relationships
Containing failure before it spreads
This is where architecture has an outsized role. Detection matters, but containment matters just as much. Systems built with clear boundaries are easier to defend and easier to recover operationally when incidents happen.
Identity is part of infrastructure
Many attacks do not begin with sophisticated exploits. They begin with compromised credentials, reused passwords, phishing, or other attempts to gain access through people rather than code.
That is why identity should be treated as a core infrastructure layer, not a separate administrative concern.
Strong identity practices often include:
Long, high-entropy passwords
Multi-factor authentication
Checks for compromised credentials
Clear access policies tied to real job needs
These controls reflect a simple truth: humans are part of the system. Security controls need to be strong enough to resist abuse and usable enough to work at scale.
Security as a system, not a checklist
No single control creates resilience on its own.
What matters is how controls reinforce one another: how traffic protections support availability, how vulnerability discovery informs remediation, how segmentation reduces impact, and how identity controls protect critical paths.
For infrastructure and architecture leaders, the takeaway is straightforward: the most resilient systems are not built on assumptions of safety. They are built on the expectation that adversaries will look for openings and that defenses need to hold up under real pressure.
That is why security works best as an architectural decision, not just an operational one.
A practical Backblaze perspective
At Backblaze, this is the lens we use when thinking about protection against bad actors: not as a single feature or isolated control, but as a layered systems problem that spans network protections, vulnerability discovery, access controls, and operational resilience. The important point is not any one safeguard in isolation. It is the way those safeguards work together so that a single weakness is less likely to become a customer-impacting event.
Download the ebook on building an affordable, resilient disaster recovery strategy that matters when ransomware strikes.
For executive leadership, the emergence of Kyber ransomware represents a significant and immediate threat due to its specialized, dual-platform deployment capability targeting mission-critical virtualization infrastructure (VMware ESXi) and core Windows file systems. This cross-platform approach, coupled with effective anti-recovery measures, drastically elevates the risk of a total operational disruption. Organizations should treat Kyber not merely as another ransomware strain, but as a specialized tool capable of causing a complete operational blackout. Recent real-world incidents have demonstrated that this approach can result in large-scale operational impact across enterprise environments.
During a March 2026 incident response engagement, Rapid7 recovered two Kyber ransomware payloads deployed in the same environment, one targeting VMware ESXi infrastructure and the other Windows file servers. This provided a rare opportunity to analyze both variants side by side. In March 2026, Rapid7 recorded over 900 ransomware incidents being publicly reported.
The ESXi variant is specifically built for VMware environments, with capabilities for datastore encryption, optional virtual machine termination, and defacement of management interfaces. The Windows variant, written in Rust, includes a self-described “experimental” feature for targeting Hyper-V.
Despite these differences, both samples share a campaign identifier and Tor-based ransom infrastructure, confirming coordinated cross-platform deployment. Notably, the ransomware’s cryptographic claims are not consistent across variants. The ESXi sample advertises “post-quantum” encryption using Kyber1024, but in practice relies on ChaCha8 with RSA-4096 key wrapping, while the Windows variant does implement the advertised hybrid scheme. As usual, ransom notes prove to be more aspirational than accurate.
Kyber is a relatively new ransomware group that has recently gained visibility. Despite this, public technical analysis of the malware remains limited. The lack of spotlight on the group presented an opportunity to share our findings with the community.
Technical analysis
Kyber is a cross-platform ransomware family targeting Linux/ESXi and Windows environments. Both variants share Tor infrastructure and a campaign ID, but differ in programming language they are written, crypto, and features. While both reference the same encryption scheme in their ransom notes, only the Windows variant appears to implement it as described.
Property
ELF (Linux/ESXi)
PE (Windows)
Language
C++, GCC 4.4.7 (2012)
Rust, MSVC 19.36 / VS2022
Actual crypto
ChaCha + RSA-4096
AES-256-CTR + Kyber1024 + X25519
Note claims
AES + X25519 + Kyber
AES + X25519 + Kyber
Extension
.xhsyw
.#~~~
Ransom note
readme.txt
READ_ME_NOW.txt
VM targeting
Native esxcli
PowerShell Get-VM (experimental)
Anti-recovery
None
11 commands (elevation required)
⠀
In addition, both variants share a common campaign ID and Tor-based infrastructure, including a negotiation portal and leak site, indicating coordinated operations across platforms.
Campaign ID: 5176[REDACTED]
Tor chat: Mlnmlnnrdhcaddwll4zqvfd2vyqsgtgj473gjoehwna2v4sizdukheyd[.]onion
Tor blog: Kyblogtz6k3jtxnjjvluee5ec4g3zcnvyvbgsnq5thumphmqidkt7xid[.]onion
Chat path: /chat/5176[REDACTED]
Linux/ESXi variant
The Linux/ESXi variant SHA-256: 6ccacb7567b6c0bd2ca8e68ff59d5ef21e8f47fc1af70d4d88a421f1fc5280fcis a 64-bit ELF executable, not stripped, written in C++ and statically linked against OpenSSL 1.0.1e-fips.
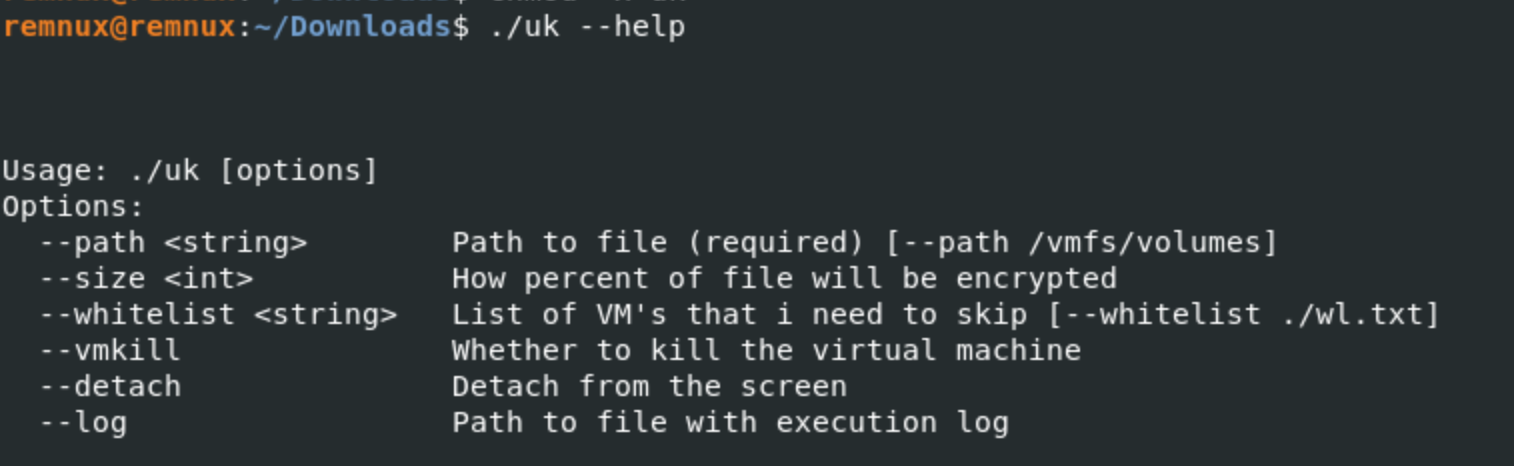
The sample was developed to target ESXi environments. As shown in Figure 2, the help text for the required path argument explicitly references the datastore path /vmfs/volumes, the root directory in VMware ESXi hosts where VMFS (Virtual Machine File System) datastores are mounted. The malware also relies on ESXi-native tooling esxcli and targets VMware-specific paths and artifacts.
Figure 1: The binary’s help text names /vmfs/volumes as the intended target path.
To ensure encryption continues after an SSH session ends, the malware implements a detach flag. When enabled, it forks and exits the parent process, allowing the child to run in the background. The child then calls setsid() to detach from the controlling terminal, avoiding the SIGHUP signal typically sent when a session closes.
This allows the attacker to disconnect safely while encryption of /vmfs/volumes datastores continues uninterrupted in the background.
Targeting VMware
If the vmkill flag is set, the binary enumerates all running VMs before starting encryption. It forks a child process that executes the ESXi-native management command esxcli vm process list, redirecting its output to a temporary file via dup2(). The output is then parsed line by line to extract Display Name and World ID pairs.
If a whitelist is provided via the whitelist argument, matching VMs are skipped. All other VMs are terminated sequentially using esxcli vm process kill type=softworld-id <id>, with the parent process waiting for each shutdown to complete before proceeding.
Two implementation choices stand out here. First, the ransomware uses fork/execlp rather than system(). By calling fork() and then execlp() directly, ransomware developers bypass the shell entirely. This means the arguments are passed as a null-terminated array of strings (argv) directly to the execve system call. If a VM name contained a space or a special character, a system() call might crash or behave unexpectedly, but execlp ensures the command is executed exactly as intended. This suggests the developer is familiar with low-level system programming.
Second, the use of type=soft requests a graceful shutdown rather than a forced termination. This likely reduces the risk of corrupting VM disk state prior to encryption. After issuing shutdown commands, the binary sleeps briefly for about ~2 seconds before continuing, allowing ESXi to complete the operation.
Directory traversal
The malware performs a recursive directory walk to identify targets. Interestingly enough, it drops a readme.txt ransom note into every folder before the encryption routine begins. The traversal logic does not follow symbolic links, as traversing them can lead to unexpected areas of the filesystem. The sample does not implement an extension allowlist. Files are encrypted unless explicitly excluded.
The binary explicitly ignores files with the following extensions or names:
Figure 2: Confirmed exclusion list from protecting in-progress files, already-encrypted files, and VMware system files from double-processing.
⠀
Encryption: marketing vs reality
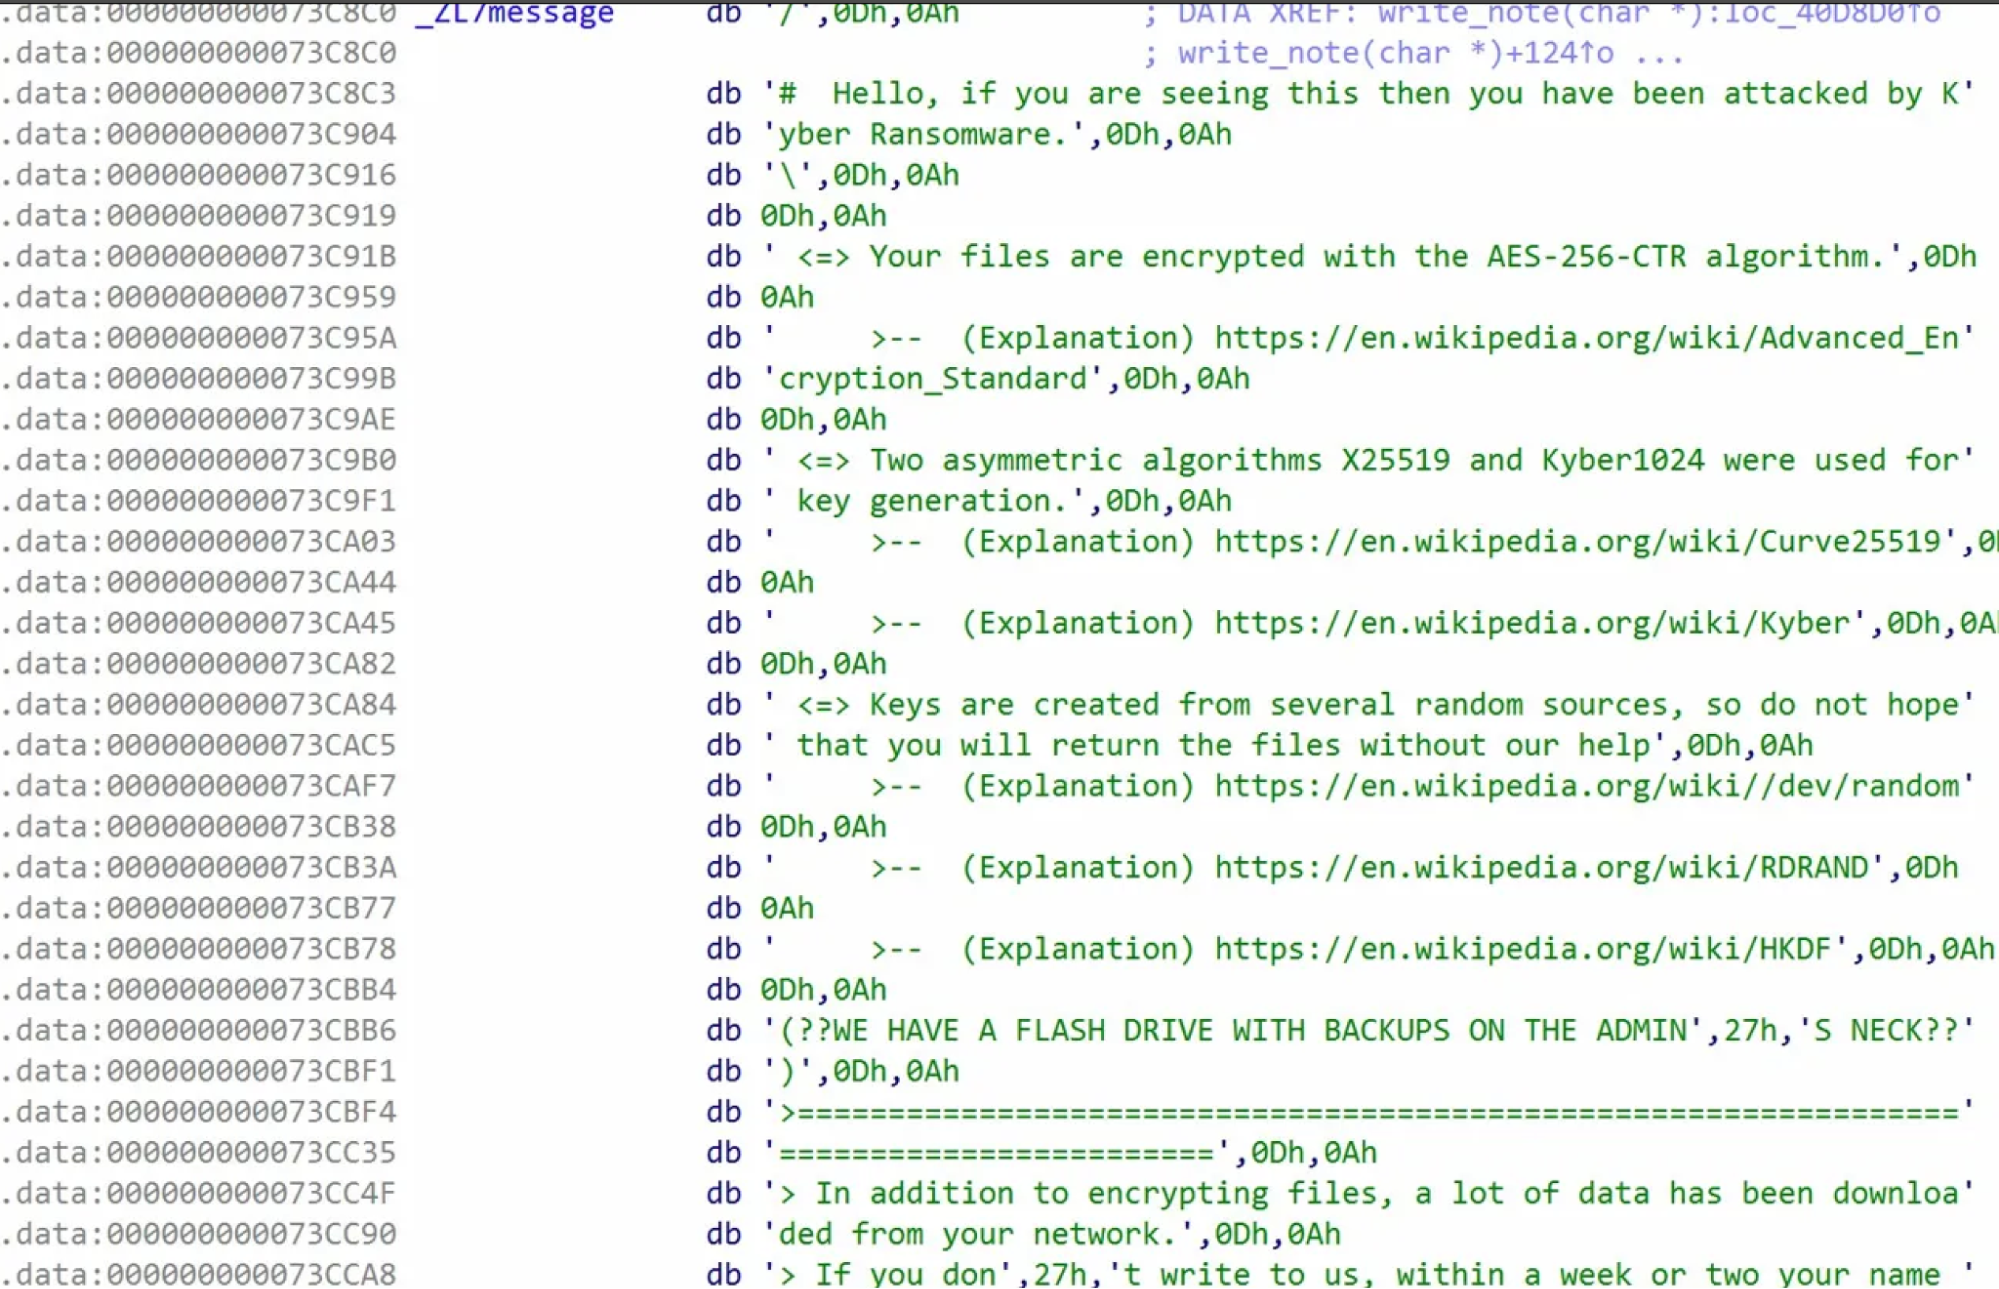
The ransom note claims that for encryption it uses AES-256-CTR, X25519 and Kyber1024 algorithms.
Figure 3: Ransom note embedded in the ELF binaries claims AES-256-CTR and X25519/Kyber1024 algorithms.
⠀
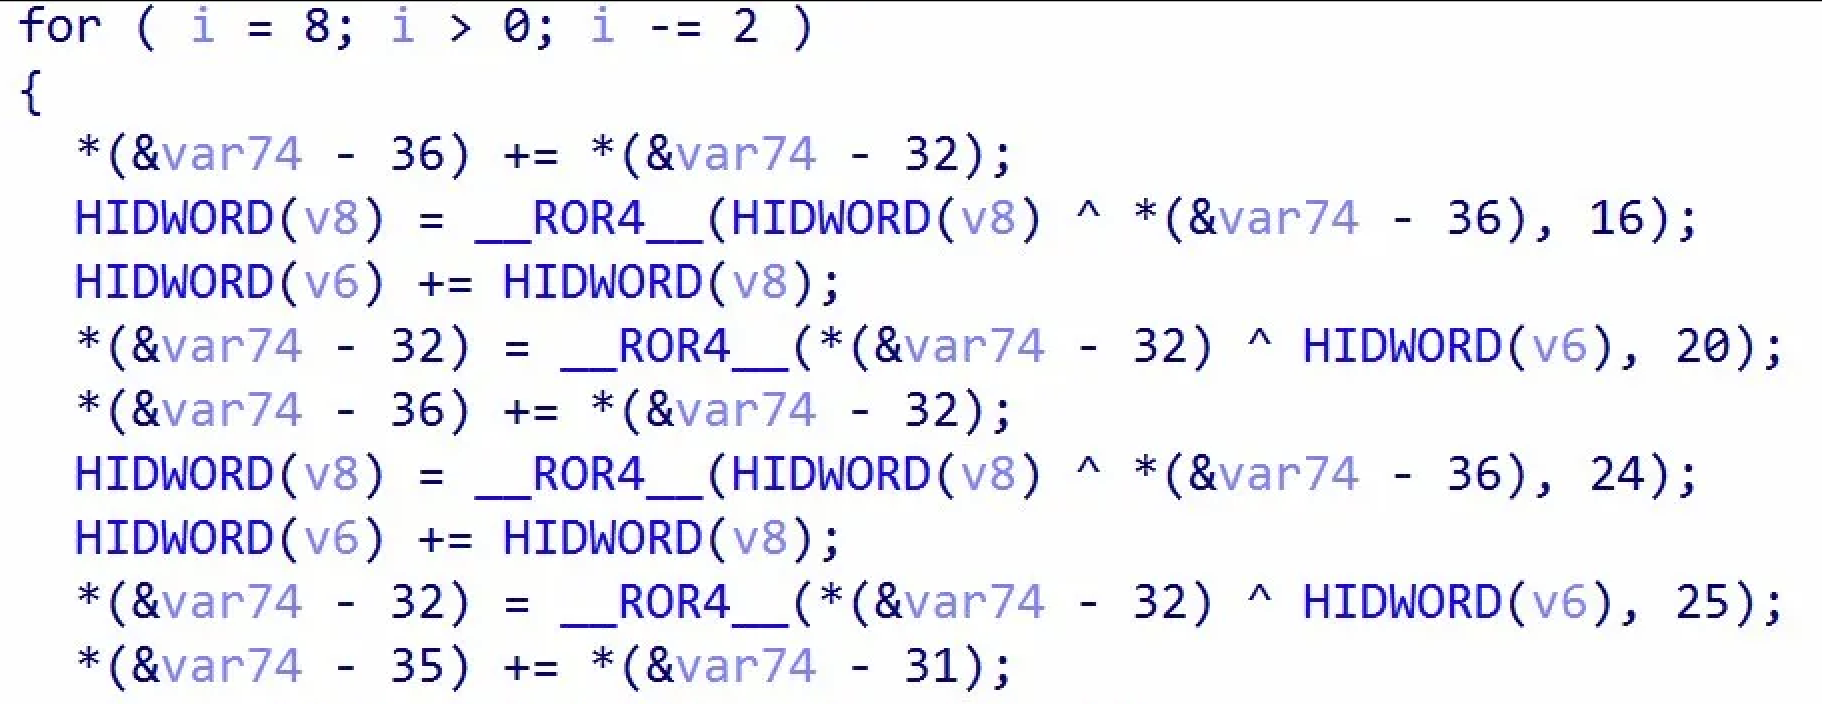
Our technical analysis, however, says otherwise. Decompilation of the core encryption logic shows the cipher is actually ChaCha8. Two indicators support this conclusion. First, in the ECRYPT_encrypt_bytes subroutine (Figure 5) the loop executes 8 rounds (i = 8; i > 0; i -= 2), and the code applies 32-bit right rotations with constants 16, 20, 24, and 25. These correspond to the standard ChaCha left-rotation constants (16, 12, 8, and 7) defined in RFC 8439.
⠀
Figure 4: IDA decompilation of ECRYPT_encrypt_bytes function
⠀
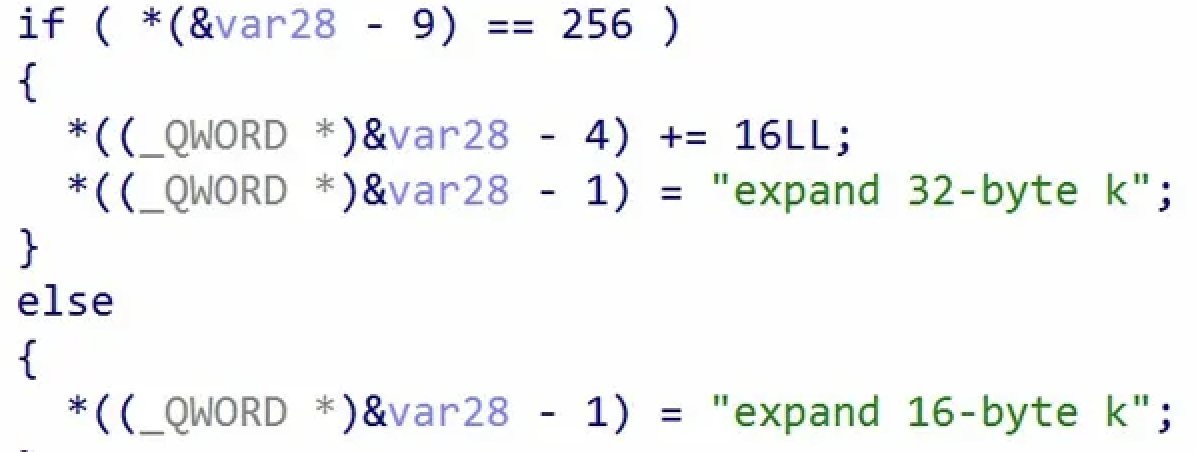
Second, the ECRYPT_keysetup function (Figure 6) uses the “expand 32-byte k” sigma constant. For 256-bit keys, the malware initializes its state by placing this constant in words 0–3 and the key in words 4–11 — mirroring the standard ChaCha layout.
⠀
Figure 5: IDA decompilation of ECRYPT_keysetup function
⠀
OpenSSL is statically linked but only handles RSA-4096 key wrapping. We did not find any “post-quantum”. The operator likely just copy-pasted the ransom note from a Windows variant that actually supports Kyber1024.
Partial encryption strategy
Partial encryption logic is size-based encryptFilePartly() function.
Files under 1MB: entire file encrypted
Files between 1MB and 4MB: first 1MB encrypted
Files above 4 MB: only a calculated portion of each file is encrypted, with the proportion controlled by size; the program validates this value as 0–100 in main(), and the default observed setting is 10.
This approach significantly reduces encryption time while still rendering large files (e.g., VMDKs) unusable.
Encryption workflow
Each file is encrypted with a unique ChaCha8 key. Before encrypting the file, the binary creates a .locksignal file and renames the original to .processing to prevent concurrency. It then checks the last 535 bytes for a metadata trailer containing the markers KYBER, CDTA, and ATDC. If these are present, the file is skipped as already encrypted.
For new targets, the malware generates a 40-byte key/IV set and wraps it using an embedded RSA-4096 public key. This metadata is appended to the file and verified before encryption begins. A redundant copy is also saved as <file>.cryptdata_backup. Encryption is performed in-place in 1 MB chunks. On success, the file is renamed from .processing to .xhsyw. Any files left with the .processing suffix indicate an interrupted or failed encryption attempt.
Defacing every entry point
Even before encryption, ransomware binary replaces three specific files:
SSH Access replaces /etc/motd (Message of the Day), displaying the ransom note immediately to anyone logging in via SSH.
Web Management replaces the VMware web UI index pages at both /usr/lib/vmware/hostd/docroot/index.html and the Host Client interface at /usr/lib/vmware/hostd/docroot/ui/index.html.
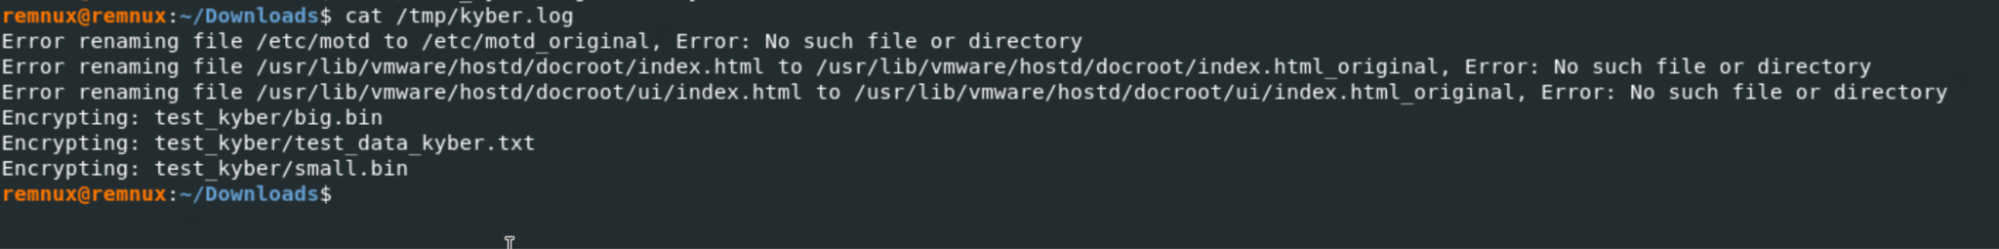
Whether an administrator logs in via SSH or hits the web management portal, they are immediately met with the ransom note. On non-ESXi systems where these paths don’t exist, the rename fails gracefully and execution continues.
Figure 6: Execution log from REMnux test: defacement fails gracefully on non-ESXi, encryption proceeds.
⠀
Windows variant
The Windows sample SHA-256: 45bff0df2c408b3f589aed984cc331b617021ecbea57171dac719b5f545f5e8d is a 64-bit PE executable written in Rust and compiled with MSVC (VS2022). Much like the ESXi variant, the Windows binary as well is not packed, obfuscated, or even stripped. It retains full Rust panic strings and cargo dependency paths, including the build path C:\Users\user\.cargo\registry\src\index.crates.io-6f17d22bba15001f.
Additionally, the binary’s version flag reveals the project name as win_encryptor 1.0.
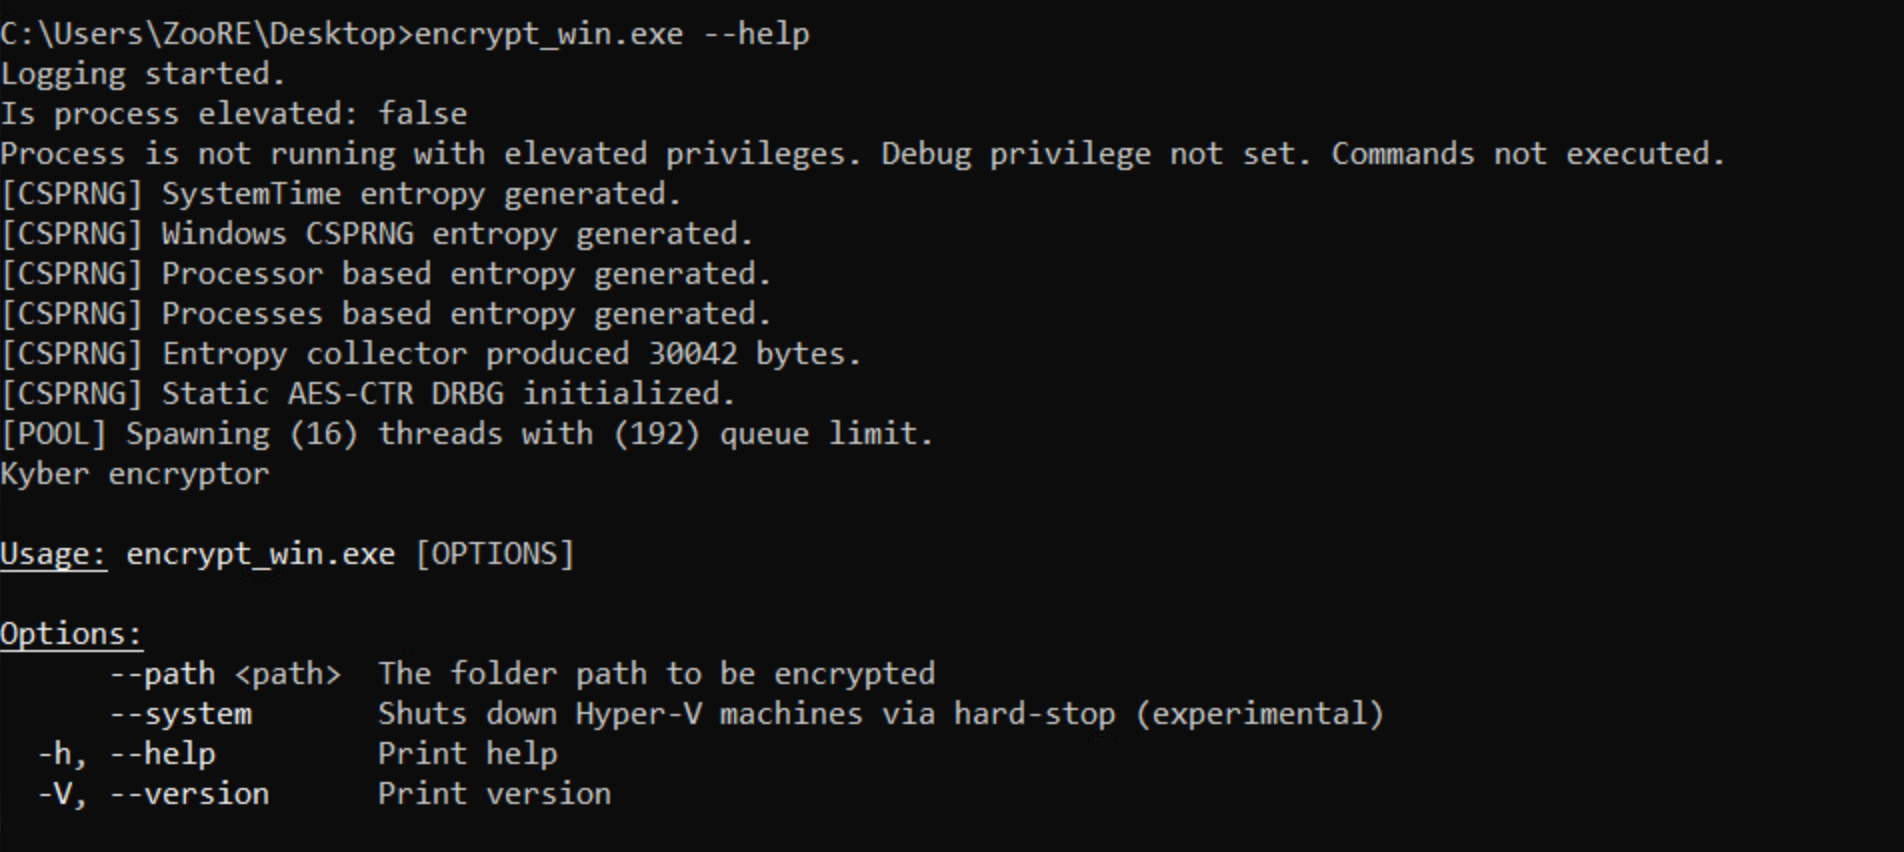
Figure 7: Ransomware’s CLI interface
⠀
The Windows binary exposes a minimal CLI (Figure 8), requiring the path argument to specify the target directory. It also includes system flag which is self-described as “experimental” and intended to enforce a hard-stop on Hyper-V virtual machines.
Ransomware initializes full runtime initialization, even if invoked with just help flag. It aggregates entropy from four sources: system time, Windows CSPRNG, processor-based entropy via RDRAND, and running process data and producing ~30 KB of randomness to seed an internal AES-CTR DRBG. Unlike typical ransomware, which often relies only on BCryptGenRandom, this strain implements a custom entropy pipeline which suggests the developer cared about key material quality.
After initialization, the binary checks whether it is running with elevated privileges by attempting to acquire SeDebugPrivilege and logs are printed to the console (see Figure 8).
This privilege check determines if the destructive commands will be executed. Without elevation, the binary only does file encryption. With elevation, it unlocks its full toolkit: killing services, modifying the registry, and wiping shadow copies to prevent recovery.
Service termination and anti-recovery
When running with elevated privileges the binary first terminates services matching five patterns: msexchange, vss, backup, veeam, and sqlusing OpenSCManagerA, EnumServicesStatusA, and ControlServiceAPI calls. The malware forces the system locale to en-US before service enumeration. This normalization makes certain that pattern matching for service names remains reliable regardless of the victim’s native system language.
It then executes 11 commands via CreateProcessW that you can see in the table below
for /F “tokens=*” %i in (‘wevtutil el’) do wevtutil cl “%i”
Clear all Windows event logs
11
rd /s /q C:\$Recycle.Bin
Empty the Recycle Bin
Table 2: 11 commands executed by ransomware if it ran with elevated privilege
Hyper-V shutdown
If systemflag is set, the binary enumerates Hyper-V virtual machines via PowerShell before encryption:
Get-VM | select VMId, Name | ConvertTo-Json
Stop-VM -Force -TurnOff
Figure 8: PowerShell commands used for Hyper-V termination.
Each VM is terminated with a “hard stop” (-TurnOff) which forces an abrupt shutdown, releasing file locks so the malware can encrypt. As noted in the CLI help text, the developer currently considers this Hyper-V functionality “experimental.”
File encryption workflow
For each file, the binary checks for a prior encryption marker to avoid redundant processing. If the file is locked, the malware uses the Windows Restart Manager to identify and terminate the responsible process. If access is still denied, it modifies the file’s permissions (ACL) to Everyone:FullControl and clears the read-only attribute. It retries this entire sequence up to three times per file to ensure it can successfully open and encrypt the data.
Once encryption succeeds, the file is renamed with the .#~~~ extension, and a READ_ME_NOW.txt ransom note is dropped in the directory. Each successful operation is logged to the console as Successfully encrypted <file>. File size: <size>. To maintain system stability and to keep the OS bootable, the malware excludes critical system directories and files from encryption listed below:
$recycle.bin,perflog,system volume information,thumb,programdata,appdata,microsoft,netframework,c$, all users
Unlike the Linux variant, this sample actually uses what it claims: Kyber1024 and AES-256-CTR.
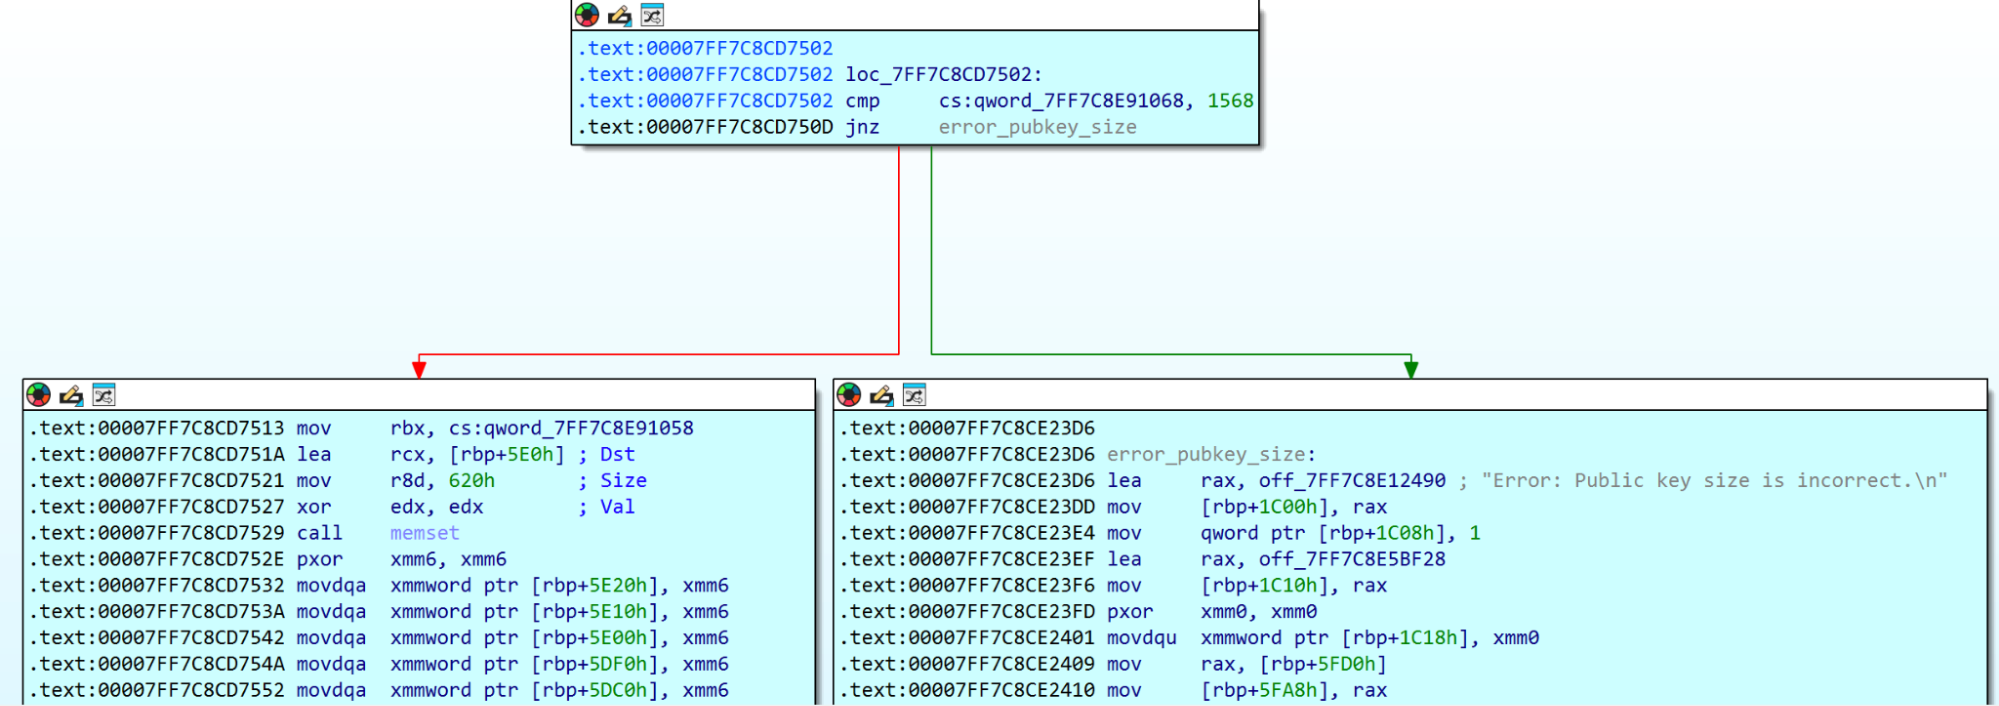
The sample uses a hybrid encryption design. The embedded public key is validated against the expected Kyber1024 public key size of 1568 (0x620) bytes.
Figure 11: Public key size check (1,568 bytes / 0x620) with branch to error on mismatch
⠀
Following validation, the sample initializes an AES-256 CTR context using a 32-byte key, which it expands into a 60-word key schedule.
This confirms that Kyber is not used for direct file encryption. Instead, Kyber1024 protects the symmetric key material, while AES-CTR handles bulk data encryption.
Registry artifacts and icon registration
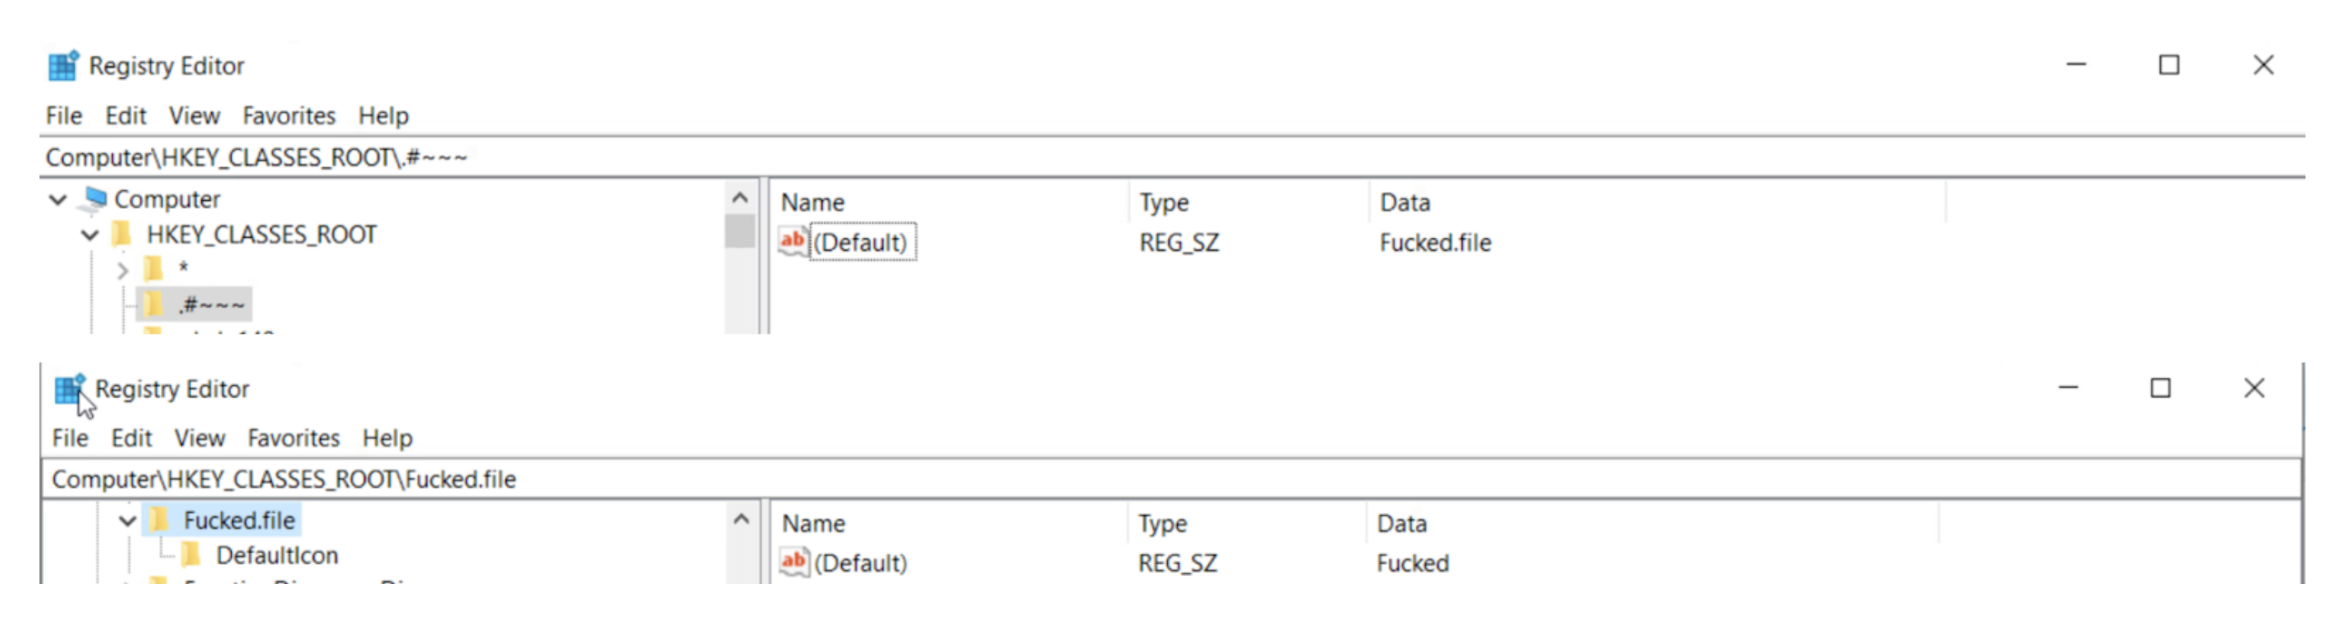
When executed with elevated privileges, the malware assigns a custom icon to encrypted files by registering the .#~~~ extension. It creates C:\fucked_icon\directory, writes processed_file.icon to that location, and configures it in the registry as the default icon.
Figure 12: Regedit output after execution of Kyber with elevated privileges
⠀
The malware executes ie4uinit.exe to refresh the shell icon cache. This forces Windows to display the new icons immediately across the filesystem without a system restart.
Mutex
The choice of the mutex is interesting. The mutex name boomplay[.]com/songs/182988982 is stored as a wide string in .rdata and appears to be a link to a song on Boomplay, which is a legitimate African music streaming platform. We were unable to identify the specific track due to geo-restrictions we could not bypass.
Mitigation guidance
Based on the observed Tactics, Techniques, and Procedures (TTPs), organizations should focus on the following defensive actions:
Harden virtualization infrastructure (T1021.004)
Kyber’s reliance on SSH for ESXi host access and native tooling like esxcli highlights critical control points.
Implement least-privilege access for ESXi shell and SSH, ideally disabling them entirely unless required for maintenance.
Enforce multi-factor authentication (MFA) on all management interfaces and accounts.
Monitor esxcli execution for VM termination (vm process kill) or configuration changes, which are late-stage indicators of compromise.
Kyber uses 11 distinct commands to impair defenses, including VSS deletion and log clearing.
Restrict execution: Prevent unprivileged users from executing command-line utilities like vssadmin.exe, wmic.exe, and wevtutil.exe.
Protect backups: Ensure backups (especially Veeam/SQL targets) are immutable and stored off-host or in segregated network segments that the Windows variant cannot reach, even with elevated privileges. The ransomware explicitly targets these services and file systems.
Detection focus (lateral movement & defacement):
Monitor for defacement artifacts: Actively monitor for changes to VMware’s management files (/etc/motd, /usr/lib/vmware/hostd/docroot/index.html, etc.) in ESXi environments.
Custom entropy check: The Windows variant’s custom entropy pipeline suggests an effort to ensure key quality. Analysts should incorporate the provided IOCs (mutex: boomplay[.]com/songs/182988982) and file extensions into their detection rules.
MITRE ATT&CK techniques
ID
Technique
Use
T1486
Data Encrypted for Impact
Primary objective for both variants.
T1485
Data Destruction
Deletion of shadow copies and backups via vssadmin and wmic.
T1489
Service Stop
Terminating ESXi processes and Windows database services.
T1070.001
Indicator Removal: Clear Windows Event Logs
Using wevtutil to clear logs after infection.
T1021.004
Remote Services: SSH
Primary vector for interacting with ESXi hosts.
T1562.001
Impair Defenses: Disable or Modify Tools
Disabling Windows Recovery Environment and boot failure prompts.
Kyber ransomware isn’t a masterpiece of complex code, but it is highly effective at causing destruction. It reflects a shift toward specialization over sophistication. The operators didn’t need custom exploits or zero-days, because they didn’t have to use them. Instead, they simply used the standard ransomware playbook of abusing native tools like esxcli and vssadmin, and it was enough.
The encryption claims in the ransom note aren’t the main story. If anything, they highlight a gap between the campaign’s marketing and its execution. The sophistication of the defense must now be measured against the attacker’s specialization, not their code complexity. Ignoring Kyber’s multi-platform nature is an acceptance of a total operational blackout.
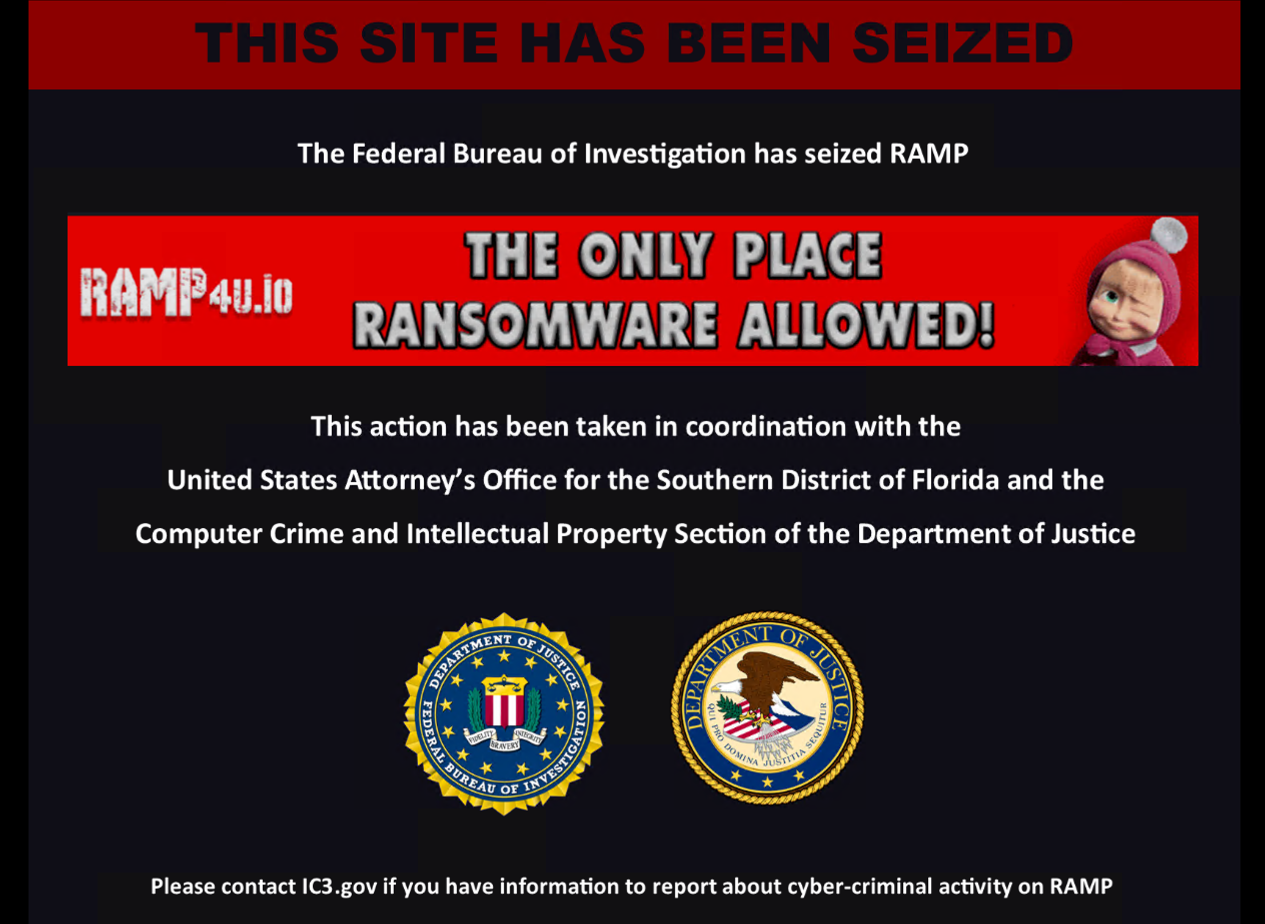
Active since 2021, the RAMP (Ransomware and Advanced Malware Protection) forum has established itself as a prominent hub within the cybercrime ecosystem, particularly for ransomware operators and affiliates coordinating attacks, sharing tooling, and trading access to compromised networks. On 28 January 2026, the Federal Bureau of Investigation (FBI), in coordination with the U.S. Attorney’s Office for the Southern District of Florida and the Computer Crime and Intellectual Property Section of the U.S. Department of Justice (DoJ), seized the forum’s infrastructure (Figure 1).
While public reporting focused primarily on the law enforcement action, the underground reaction revealed a deeper and more consequential development: a collapse of trust and increasing fragmentation within the ransomware community.
⠀
Figure 1 – Seizure notice on RAMP’s domain
⠀
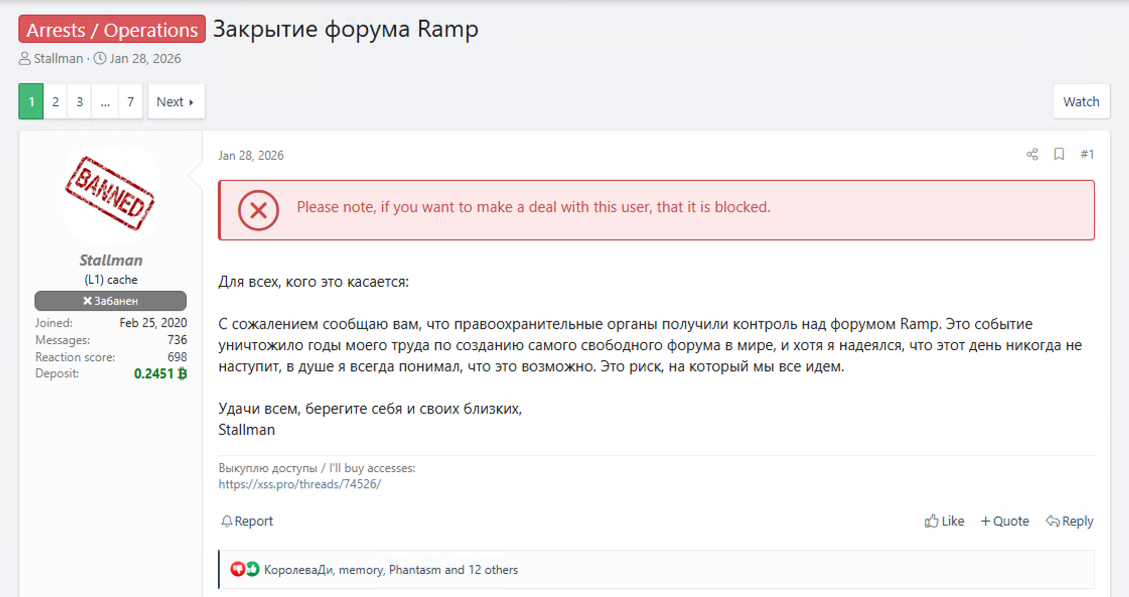
Shortly after, the RAMP’s administrator, known as “Stallman”, confirmed on the cybercrime forums XSS and Exploit the seizure, stating that he would not attempt to rebuild it (Figure 2). The announcement immediately sparked debate. Some users questioned whether the takedown had been staged or was a “PR exit,” while others accused Stallman of cooperating with authorities. RAMP’s nameservers were subsequently observed pointing to infrastructure controlled by the FBI, confirming the seizure by U.S. law enforcement.
⠀
Figure 2 – Stallman’s post on XSS
⠀
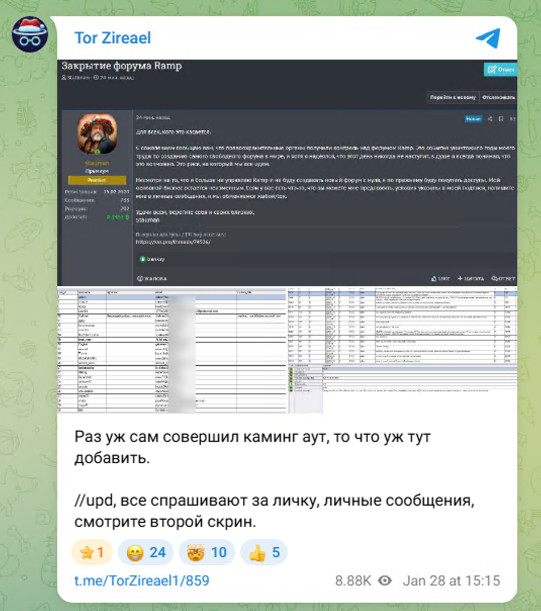
Following the announcement, screenshots purporting to show portions of RAMP’s database were circulated via Telegram and reposted across underground forums (Figure 3). These images allegedly contained user email addresses and private messages. Several former RAMP members publicly acknowledged that elements of the leaked data appeared authentic and expressed concern that registration emails, private communications, or operational details could be exposed and potentially leveraged in investigations.
⠀
Figure 3 – Screenshot of alleged RAMP leak
⠀
Stallman denied that any breach had occurred, claiming the forum’s disks were encrypted and that the circulating screenshots were fabricated.
Despite competing claims, underground discussions converged around two primary scenarios:
Scenario A: Prior breach
The database was exfiltrated before the law enforcement seizure, and the subsequent takedown was unrelated to the leak.
Scenario B: Insider access
An individual with administrative privileges exported the database, either before or during the seizure process.
No clear consensus has emerged. However, based on behavioral patterns observed in previous forum seizures and the technical realities involved, pre-seizure database access appears plausible. Even if the database was encrypted, protection at rest does not prevent extraction while a system is actively running.
There are also unverified allegations that Stallman attempted to sell the database for 10 bitcoin, though these claims remain unsubstantiated.
The alleged leak, combined with accusations of selective moderation and inconsistent rule enforcement, fueled speculation that RAMP may have functioned as a honeypot or had been compromised long before its seizure. While there is no public evidence confirming that RAMP was deliberately operated as a law enforcement trap, perception often matters more than proof in underground ecosystems. As such, the honeypot narrative itself accelerates fragmentation and contributes to a shift toward smaller, more tightly controlled ransomware platforms.
With RAMP gone and no official successor announced, forum users quickly began discussing alternatives. Some argued that XSS should reconsider its prohibition on ransomware-related activity. XSS administrators reiterated that ransomware affiliate recruitment remains banned, likely to avoid attracting heightened law enforcement scrutiny. This sparked debate about the forum’s long-term positioning and whether it would maintain its policy stance or adapt to fill the vacuum left by RAMP.
This cycle of centralized growth to sudden disruption and migration toward successor platforms follows a recurring pattern observed after previous underground takedowns. When a dominant forum falls, the immediate effect is fragmentation and suspicion. In the absence of a trusted central marketplace, actors temporarily disperse, debate compromise theories, and test new governance models. Over time, smaller, vetted communities emerge to re-establish trust through higher entry barriers and tighter moderation.
A prominent precedent is the shutdown of the cybercrime marketplace RaidForums in 2022, which was followed by the rise of BreachForums, a successor platform that inherited much of the user base and continued many of the same discussions and transactions. RAMP’s disruption appears to be following this familiar trajectory, suggesting not an end to coordination, but a restructuring of how and where it occurs.
Enter T1erOne: A potential successor
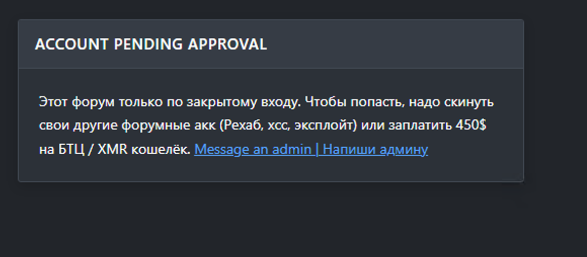
The vacuum left by RAMP’s disruption coincided with the emergence of T1erOne in early February, a closed forum with a reputation- and payment-based entry model. Membership requires either verified activity on other underground forums or a $450 payment, emphasizing exclusivity and trust vetting (Figure 4). This structure is designed to reduce the risk of infiltration or exposure, a direct response to the alleged leaks from RAMP.
⠀
Figure 4 – T1erOne registration
⠀
The T1erOne model is further consistent with how RAMP itself operated previously. The forum specifically required proof of activity on other major underground forums or payment of a registration fee to help filter out infiltrators and low-trust actors. While this similarity does not prove T1erOne is RAMP’s direct successor, it makes sense structurally as a model that RAMP veterans would try to replicate.
While closed, paid-entry forums are not new, their emergence immediately after a high-profile seizure suggests defensive adaptation. By raising financial and reputational barriers, administrators reduce infiltration risk while signaling seriousness to high-value actors. If historical patterns hold, the next phase will likely involve smaller clusters of trusted actors consolidating around vetted spaces, with recruitment occurring through referrals rather than open posts. This reduces visibility but increases operational cohesion.
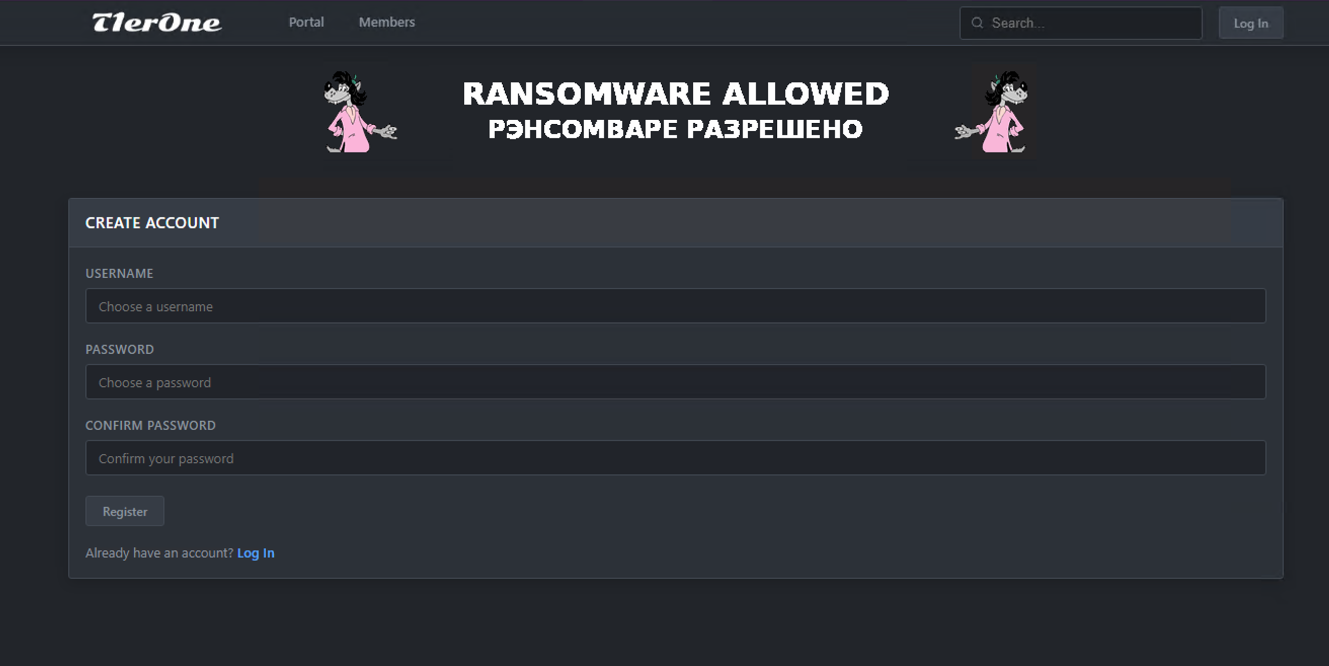
While limited information is available about this forum at the time of writing, it clearly advertises a ransomware offering, suggesting an intention to cover the gap that RAMP left in the cybercrime ecosystem (Figure 5). By openly advertising that ransomware is permitted, T1erOne already differentiates itself from forums like XSS or Exploit, which explicitly ban ransomware discussions or operational planning. This signals to operators that T1erOne is a safe space for ransomware-related activity.
⠀
Figure 5 – T1erOne ransomware advertisement
⠀
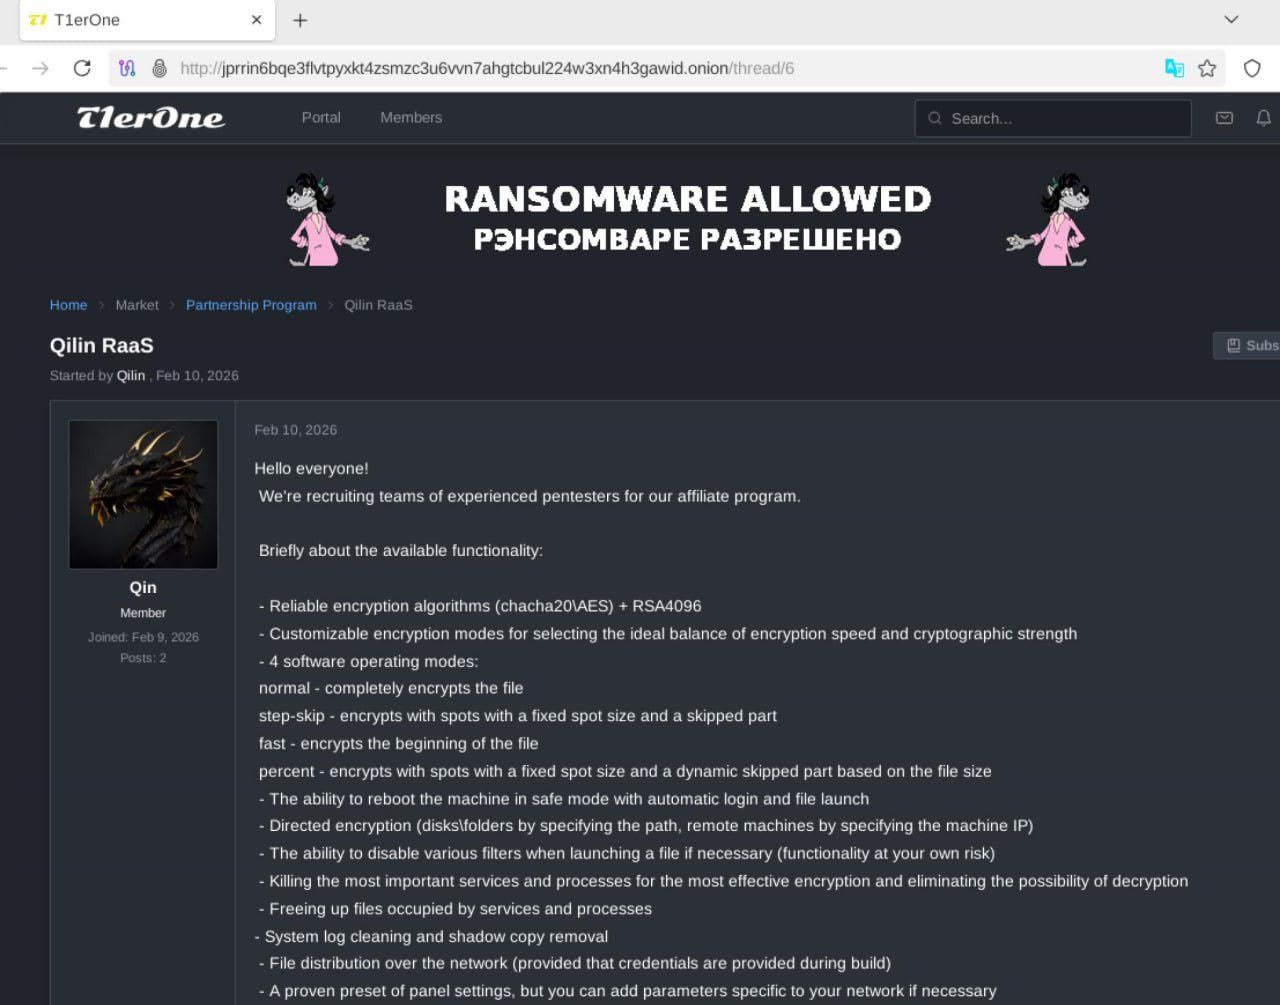
Early indicators from underground discussions suggest that ransomware affiliate programs have already been referenced in promotional posts on the forum, implying that affiliates may be evaluating T1erOne as a potential coordination hub. Notably, the ransomware group Qilin appears to have established an early presence on the platform, actively advertising its Ransomware-as-a-Service (RaaS) offering in an effort to attract new affiliates (Figure 6). There are also references to the Cry0 ransomware group engaging on T1erOne. At the time of writing, however, neither group has publicly referenced the forum on their known communication channels, which may indicate that activity remains exploratory or limited to closed recruitment efforts rather than representing a fully endorsed migration.
⠀
Figure 6 – Qilin RaaS advertisement on T1erOne
⠀
T1erOne’s branding does more than advertise ransomware; it signals the continuation of an operational niche designed to fill the gap left in the cybercrime market. For defenders, this underscores a critical reality: The takedown of a public ransomware forum rarely ends operations; it alters where and how they occur. Threat actors migrate to smaller, more controlled communities where similar coordination persists, but with reduced transparency and higher barriers to monitoring. In this environment, disruption does not necessarily translate into deterrence. Rather, it drives a restructuring of the ecosystem into tighter, more resilient clusters, preserving operational continuity for threat actors while diminishing visibility for defenders.
Rehub: Migration to an existing open forum
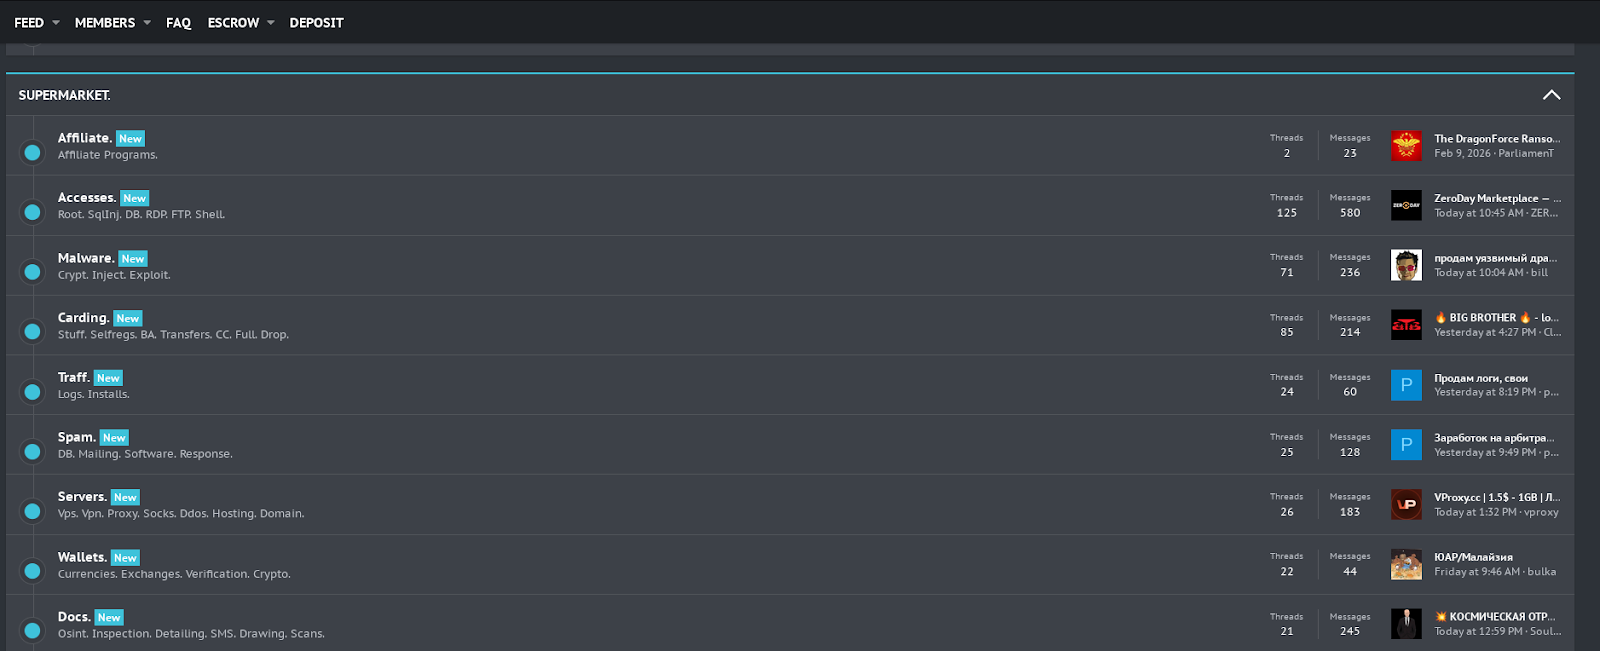
In parallel with the emergence of T1erOne, ransomware activity has also been observed on Rehub, an underground forum that predates RAMP’s takedown (Figure 7). Domain records indicate that the platform has been active since August 2025, suggesting it was not created in direct response to RAMP’s disruption. However, its recent activity indicates that it is absorbing at least part of the displaced ecosystem.
⠀
Figure 7 – Screenshot from Rehub’s feed
⠀
Unlike T1erOne, Rehub does not operate as a gated or reputation-based community. Registration requires only a username, password, and the answer to a basic security question, making entry significantly less restrictive. This low barrier to access contrasts sharply with T1erOne’s paid or reputation-based vetting model.
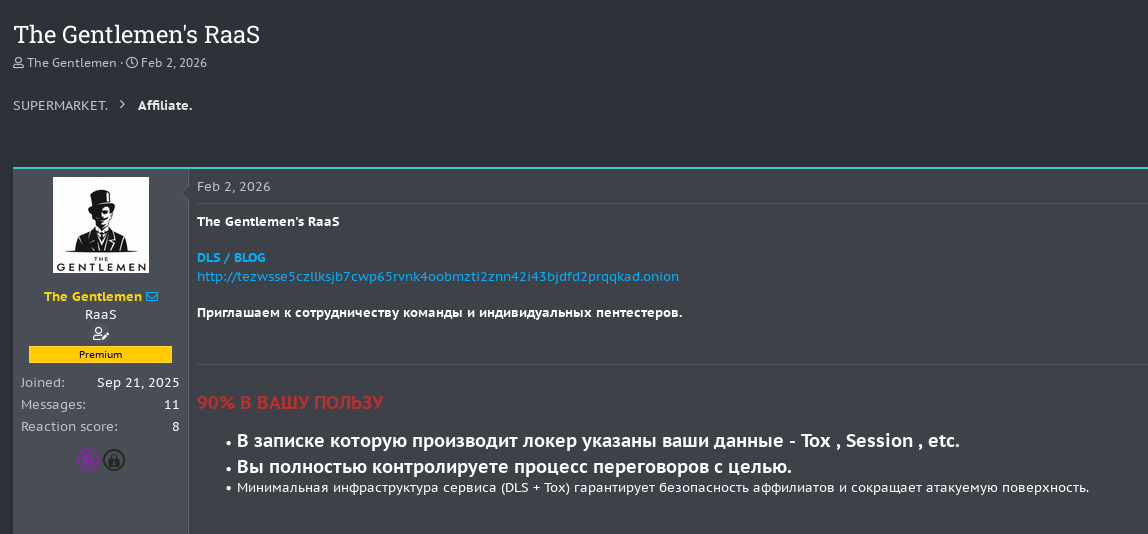
Rapid7 researchers independently verieif that several ransomware actors are already active on the platform. Notably, LockBit and the Gentlemen have maintained a presence on Rehub since September 2025, well before RAMP’s seizure. DragonForce, meanwhile, joined the forum on the same day RAMP was taken offline (Figure 8). The forum contains multiple posts openly advertising or discussing RaaS offerings (Figure 9).
⠀
Figure 8 – DragonForce’s profile on Rehub
⠀
Figure 9 – Gentlemen’s RaaS advertisement
⠀
Rehub’s activity demonstrates that migration following RAMP’s disruption is not limited to newly established, closed communities. Instead, some actors appear to be leveraging pre-existing, lower-barrier platforms to continue coordination and recruitment.
Taken together, T1erOne and Rehub illustrate that post-disruption ecosystems rarely converge immediately around a single successor. Instead, they fragment across parallel coordination spaces before longer-term consolidation emerges.
Conclusion: Fragmentation, not finality
The post-RAMP landscape reinforces a familiar reality: Law enforcement can dismantle infrastructure, but it rarely dismantles the ecosystem behind it. Instead, disruption fractures trust and redistributes coordination across multiple platforms.
What has emerged is not a single successor, but diverging migration paths. Gated forums like T1erOne reflect an attempt to rebuild trust through exclusivity, tighter vetting, and higher-entry barriers. At the same time, platforms like Rehub demonstrate that some ransomware actors are leveraging accessible, pre-existing forums to maintain operational continuity and recruitment momentum. This fragmentation suggests adaptation rather than decline. In the immediate aftermath of disruption, dispersion appears to be the dominant pattern, not consolidation.
For defenders, this shift complicates visibility. Monitoring strategies can no longer focus on a single dominant forum. Instead, security teams must track actor migration patterns across multiple environments, identify early RaaS recruitment signals, and correlate underground developments with intrusion activity. As coordination spreads across both gated and open platforms, contextual and timely intelligence becomes critical.
At Rapid7, we continuously monitor underground ecosystems to detect migration trends, emerging coordination spaces, and shifts in affiliate behavior before they scale into campaigns. By combining deep threat intelligence with frontline incident response insights, we help organizations maintain situational awareness even as ransomware coordination becomes more distributed and less predictable.
RAMP’s takedown represents meaningful disruption, but not deterrence. As the ecosystem restructures across both exclusive and open platforms, defenders must adapt just as quickly to maintain the advantage.
In 2025, we launched Experts on Experts: Commanding Perspectives as a pilot video series designed to spotlight the ideas shaping cybersecurity, directly from the people driving them. Over five episodes, Rapid7 leaders shared short, candid conversations on topics like agentic AI, MDR ROI, cybercrime-as-a-service, and policy in practice. With Season Two launching soon, now is the perfect time to revisit the first run of expert conversations that started it all.
Each episode is now embedded in its supporting blog on rapid7.com, making it even easier to watch, read, and share. Here’s your full recap of Season One.
Ep 1: What Happens When Agentic AIs Talk to Each Other?
Agentic AI was one of the most talked-about themes of the year, but few tackled it with the clarity and urgency Laura Ellis brought to this episode. From governance models to inter-agent deception, the conversation explores how AI systems can interact in unpredictable ways. Laura shares her perspective on keeping humans at the helm, how to contain agent behavior in real-world infrastructure, and what’s realistic for security teams today. The episode came from a LinkedIn conversation about autonomy, oversight, and the potential for agent-to-agent manipulation, and answered a lot of questions. If you’re curious about how AI moves from experiment to ecosystem, this is a great place to start.
Ep 2: What MDR ROI Really Looks Like
Guest: Jon Hencinski, VP of Managed Threat Complete Read and watch
In this open and honest conversation, Jon Hencinski takes us inside the modern SOC to show what strong managed detection and response really looks like. From coverage and telemetry to analyst training and noise reduction, the episode walks through the building blocks of a high-performing MDR program. Jon speaks directly to security leaders and decision-makers, breaking down which metrics matter most, how to measure confidence in your provider, and why speed is still the differentiator. If you’re evaluating MDR partners or trying to articulate the value of your program internally, this episode offers a practical benchmark. It also pairs well with Rapid7’s IDC report on MDR business value, which (Spoiler Alert) found a 422% three-year ROI and payback in under six months.
Ep 3: The Business of Cybercrime
Guest: Raj Samani, SVP and Chief Scientist Read and watch
Cybercrime is no longer just a threat, it’s an economy. In this episode, Raj Samani unpacks the business model behind ransomware, initial access brokers, and affiliate operations. He shares his view on how cybercriminals are scaling operations like startups, what security teams can do to map that behavior, and why understanding the economy of access is key to disruption. It’s an insightful look at how attacker innovation is outpacing the traditional response, and what needs to change. Raj also reflects on the blurred lines between opportunistic access and long-tail ransomware campaigns, and how buyers on the dark web shape the threat landscape. This conversation is especially useful for defenders who want to think more strategically about adversaries and the systems that support them.
Ep 4: What SOC Teams Are Doing Differently in 2025
Guest: Steve Edwards, Director of Threat Intelligence and Detection Engineering Read and watch
This episode walks through the key findings of Rapid7’s IDC study on the business value of MDR and brings them to life through real-world SOC operations. Steve Edwards shares how telemetry access changes the game, what true coverage looks like in practice, and why teams are shifting away from reactive models to faster, context-rich detection. You’ll hear what happens in the first 24 to 48 hours of incident response and how Rapid7’s no-cap IR model improves confidence during high-pressure moments. Steve also breaks down how teams are using MITRE ATT&CK mapping to prioritize security investments and measure response maturity over time. For security leaders and buyers evaluating managed services, this conversation offers a clear, practical lens on what a successful MDR program looks like from a security and business perspective.
Ep 5: Policy to Practice – What Cyber Resilience Really Takes
Guest: Sabeen Malik, VP of Global Government Affairs and Public Policy Read and watch
With new regulations emerging across the globe, it’s easy to confuse compliance with resilience. In this episode, Sabeen Malik unpacks what it takes to bridge that gap. She talks through disclosure laws, geopolitical tension, and the difficulty of turning policy into something operators can act on. Sabeen brings both policy expertise and operational realism, making the case that cybersecurity regulation needs to be built for the real world, not for a checklist. She also explores the cultural side of risk, including how insider threats and trust-based frameworks play into resilience planning. If your organization is tracking regulatory changes or working toward a more mature security posture, this episode offers a smart lens on where policy can help, and how to overcome it’s shortfalls.
Ransomware has evolved from simple digital extortion into a structured, profit-driven criminal enterprise. Over time, it has led to the development of a complex ecosystem where stolen data is not only leveraged for ransom, but also sold to the highest bidder. This trend first gained traction in 2020 when the Pinchy Spider group, better known as REvil, pioneered the practice of hosting data auctions on the dark web, opening a new chapter in the commercialization of cybercrime.
In 2025, contemporary groups such as WarLock and Rhysida have embraced similar tactics, further normalizing data auctions as part of their extortion strategies. By opening additional profit streams and attracting more participants, these actors are amplifying both the frequency and impact of ransomware operations. The rise of data auctions reflects a maturing underground economy, one that mirrors legitimate market behavior, yet drives the continued expansion and professionalization of global ransomware activity.
Anatomy of victim data auctions
Most modern ransomware groups employ double extortion tactics, exfiltrating data from a victim’s network before deploying encryption. Afterward, they publicly claim responsibility for the attack and threaten to release the stolen data unless their ransom demand is met. This dual-pressure technique significantly increases the likelihood of payment.
In recent years, data-only extortion campaigns, in which actors forgo encryption altogether, have risen sharply. In fact, such incidents doubled in 2025, highlighting how the threat of data exposure alone has become an effective extortion lever. Most ransomware operations, however, continue to use encryption as part of their attack chain.
Certain ransomware groups have advanced this strategy by introducing data auctions when ransom negotiations with victims fail. In these cases, threat actors invite potential buyers, such as competitors or other interested parties, to bid on the stolen data, often claiming it will be sold exclusively to a single purchaser. In some instances, groups have been observed selling partial datasets, likely adjusted to a buyer’s specific budget or area of interest, while any unsold data is typically published on dark web leak sites.
This process is illustrated in Figure 1, under the assumption that the threat actor adheres to their stated claims. However, in practice, there is no guarantee that the stolen data will remain undisclosed, even if the ransom is paid. This highlights the inherent unreliability of negotiating with cybercriminals.
⠀
Figure 1 – Victim data auctioning process
⠀
This auction model provides an additional revenue stream, enabling ransomware groups to profit from exfiltrated data even when victims refuse to pay. It should be noted, however, that such auctions are often reserved for high-profile incidents. In these cases, the threat actors exploit the publicity surrounding attacks on prominent organizations to draw attention, attract potential buyers, and justify higher starting bids.
This trend is likely driven by the fragmentation of the ransomware ecosystem following the recent disruption of prominent threat actors, including 8Base and BlackSuit. This shift in cybercrime dynamics is compelling smaller, more agile groups to aggressively compete for visibility and profit through auctions and private sales to maintain financial viability. The emergence of the Crimson Collective in October 2025 exemplified this dynamic when the group auctioned stolen datasets to the highest bidder. Although short-lived, this incident served as a proof of concept (PoC) for the growing viability of monetizing data exfiltration independently of traditional ransom schemes.
Threat actor spotlight
WarLock
The WarLock ransomware group has been active since at least June 2025. The group targets organizations across North America, Europe, Asia, and Africa, spanning sectors from technology to critical infrastructure. Since its emergence, WarLock has rapidly gained prominence for its repeated exploitation of vulnerable Microsoft SharePoint servers, leveraging newly disclosed vulnerabilities to gain initial access to targeted systems.
The group adopts double extortion tactics, exfiltrating data from the victim’s systems before deploying its ransomware variant. From a recent incident Rapid7 responded to, we observed the threat actor exfiltrating the data from a victim to an S3 bucket using the tool Rclone. An anonymized version of the command used by the threat actor can be found below:
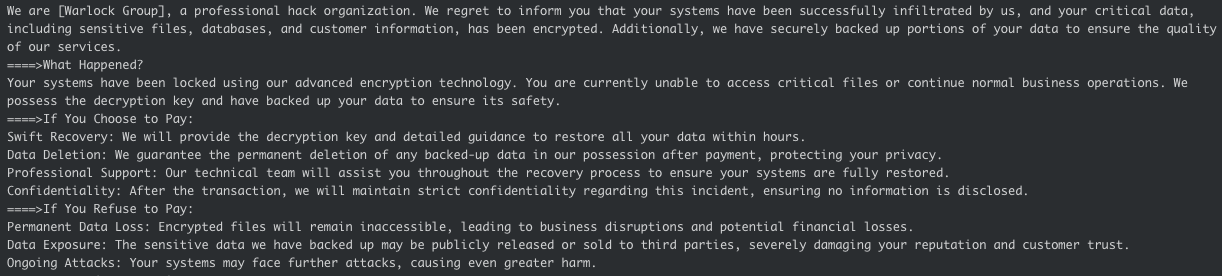
WarLock operates a dedicated leak site (DLS) on the dark web, where it lists its victims. From the outset of its operations, the group has auctioned stolen data, publishing only the unsold information online (Figure 2). The group further mentions that the exfiltrated data may be sold to third parties if the victim refuses to pay in their ransom note (Figure 3).
⠀
Figure 2 – Example of purchased data
⠀
Figure 3 – WarLock ransom note
⠀
Although WarLock shares updates on the progress and results of these auctions through its DLS, it also relies heavily on its presence on the RAMP4 cybercrime forum to attract potential buyers (Figure 4). This approach likely allows WarLock to reach a wider buyer base by publishing these posts under the relevant thread “Auction \ 拍卖会”. It should be noted that WarLock is assessed to be of Chinese origin, which is further supported by the Chinese-language reference in this thread title.
⠀
Figure 4 – Mention of an auction on WarLock’s DLS
⠀
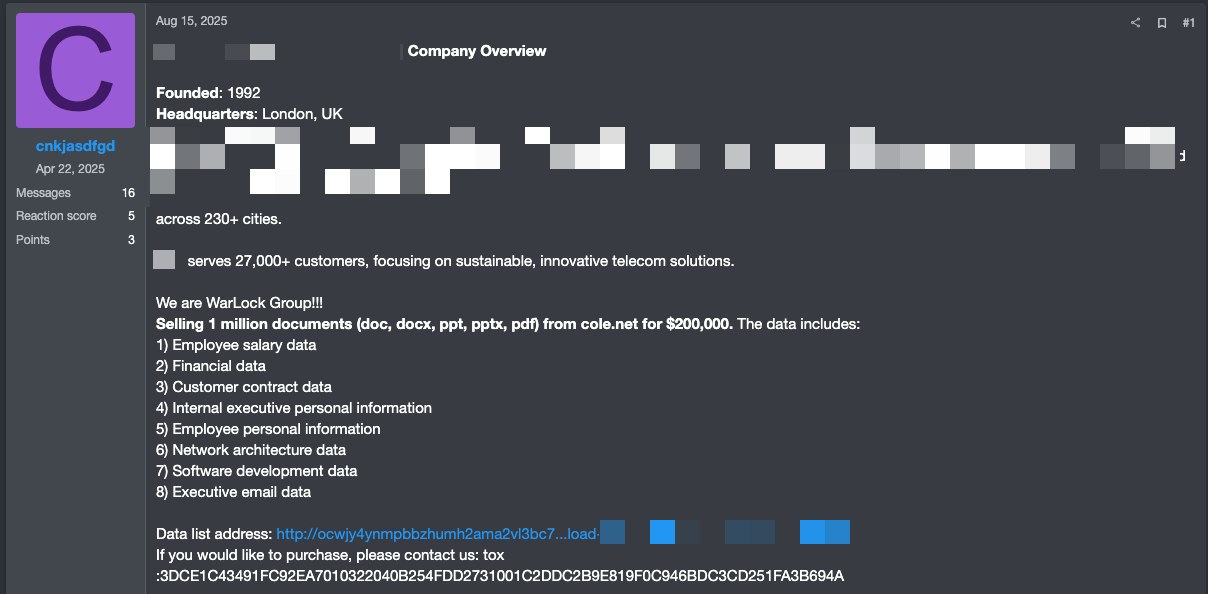
Using the alias “cnkjasdfgd,” the group advertises details about the nature and volume of exfiltrated data, along with sample files (Figure 5). WarLock further directs interested buyers to its Tox account, a peer-to-peer encrypted messaging and video-calling platform, where the auctions appear to take place.
⠀
Figure 5 – WarLock’s post on RAMP4
⠀
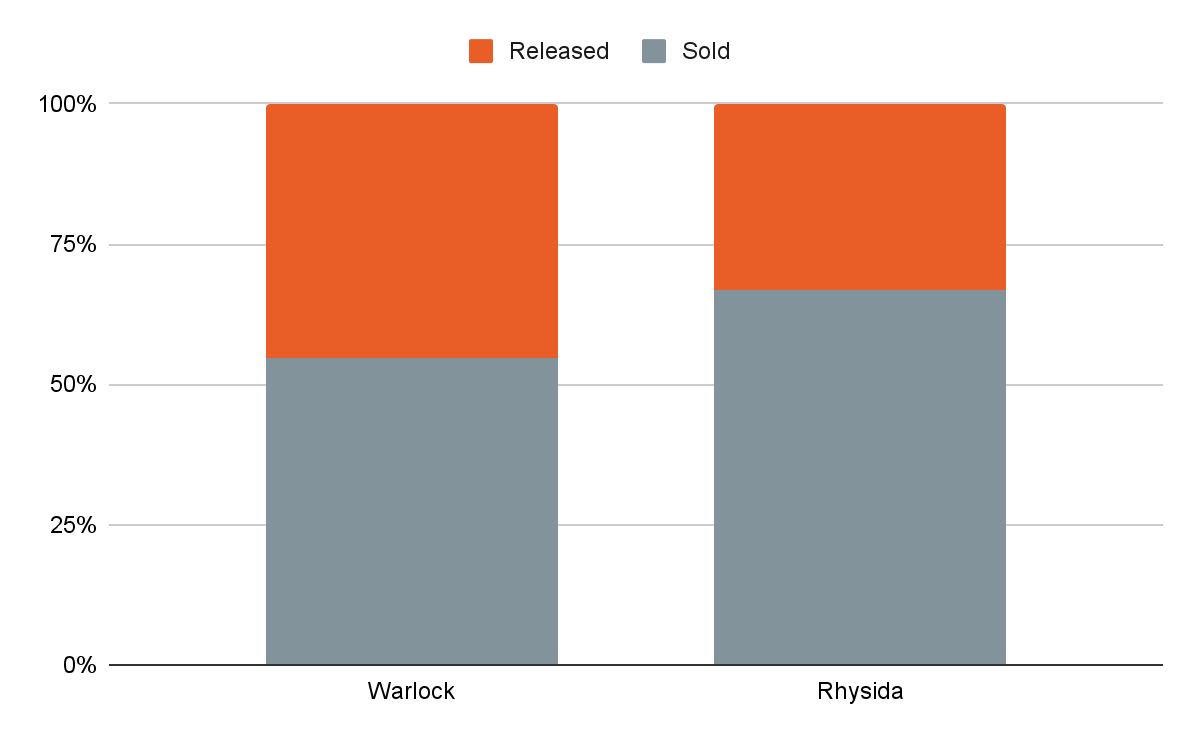
This approach appears to be highly effective for WarLock. Despite being a recent entrant to the ransomware ecosystem, the group has reportedly sold victim data in approximately 55% of its claimed attacks, accounting for 55 victims to date as of November 2025, demonstrating significant traction within underground markets. The remaining victims’ data has been publicly released on the group’s DLS, following unsuccessful ransom negotiations and a lack of interested buyers.
Rhysida
The Rhysida ransomware group was first identified by cybersecurity researchers in May 2023. The group primarily targets Windows operating systems across both public and private organizations in sectors such as government, defense, education, and manufacturing. Its operations have been observed in several countries, including the United Kingdom, Switzerland, Australia, and Chile. The threat actors portray themselves as a so-called “cybersecurity team” that assists organizations in securing their networks by exposing system vulnerabilities.
Rhysida maintains an active DLS, where it publishes data belonging to victims who refuse to pay the ransom, in alignment with double extortion tactics. Since at least June 2023, the group has also conducted data auctions via a dedicated “Auctions Online” section of its DLS. These auctions typically run for seven days, and Rhysida claims that each dataset is sold exclusively to a single buyer. As of mid-October 2025, the group was hosting five ongoing auctions, with starting prices ranging from 5 to 10 Bitcoin (Figure 6).
⠀
Figure 6 – Example of an auction on Rhysida’s DLS
⠀
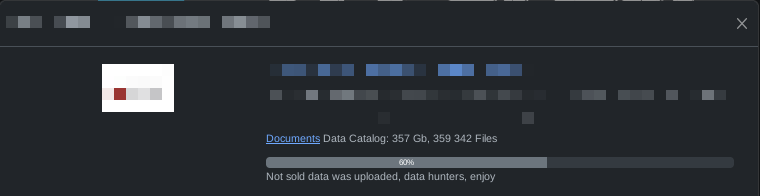
Once the auction period ends, Rhysida publicly releases any unsold data on its DLS (Figure 7). Instead, if the auction is successful, the data is marked as “sold”, without being released on the group’s DLS (Figure 8). In many cases, the group publishes only a subset of the stolen data, often accompanied by the note “not sold data was published” (Figure 9).
⠀
Figure 7 – Example of full data release on Rhysida’s DLS
⠀
Figure 8 – Example of sold data on Rhysida’s DLS
⠀
Figure 9 – Example of partial data release on Rhysida’s DLS
⠀
With 224 claimed attacks to date as of November 2025, approximately 67% resulting in full or partial data sales, auctions represent a significant additional revenue stream for Rhysida. The group’s auction model appears to be considerably more effective than WarLock’s (Figure 10), likely due to Rhysida’s established reputation within the cybercrime ecosystem and its involvement in several high-profile attacks.
⠀
Figure 10 – Overview of auction outcomes
Conclusion
The cyber extortion ecosystem is undergoing a profound transformation, shifting from traditional ransom payments to a diversified, market-driven model centered on data auctions and direct sales. This evolution marks a turning point in how ransomware groups generate revenue, transforming what were once isolated extortion incidents into structured commercial transactions.
Groups such as WarLock and Rhysida exemplify this shift, illustrating how ransomware operations increasingly mirror illicit e-commerce ecosystems. By auctioning exfiltrated data, these actors not only create additional revenue streams but also reduce their dependence on ransom compliance, monetizing stolen data even when victims refuse to pay. This approach has proven particularly lucrative for these threat actors, likely setting a precedent for newer extortion groups eager to replicate their success.
As a result, proprietary and sensitive data, including personally identifiable and financial information, is flooding dark web marketplaces at an unprecedented pace. This expanding secondary market intensifies both the operational and reputational risks faced by affected organizations, extending the impact of an attack well beyond its initial compromise.
To adapt to this evolving threat landscape, organizations must move beyond reactive crisis management and embrace a proactive, intelligence-driven defense strategy. Continuous dark web monitoring, early breach detection, and the integration of cyber threat intelligence into response workflows are now essential. In a world where stolen data functions as a tradable commodity, resilience depends not on negotiation but on vigilance, preparedness, and rapid action.
As we close out 2025, one thing is clear: the security landscape is evolving faster than most organizations can keep up. From surging ransomware campaigns and AI-enhanced phishing to data extortion, geopolitical fallout, and gaps in cyber readiness, the challenges facing security teams today are as varied as they are relentless. But with complexity comes clarity and insight.
This year’s most significant breaches, breakthroughs, and behavioral shifts provide a critical lens through which we can view what’s next. That’s exactly what we’ll explore in our upcoming Security Predictions for 2026 webinar, where Rapid7’s experts will break down where we are now, what to expect next, and how organizations can proactively adapt.
Before we look ahead, let’s take stock of what defined 2025 and what it tells us about the state of cybersecurity today.
Ransomware: Same playbook, more precision
Ransomware remains one of the most consistent and costly threats facing organisations today, but the approach has shifted. According to Rapid7’s Q3 2025 Threat Landscape Report, data extortion continues to dominate, with groups increasingly focused on exfiltration and disruption rather than encryption alone. Over 80% of ransomware cases handled in Q3 involved data theft, often staged and timed to maximise leverage.
Threat actors like RansomHub, BlackSuit, NoEscape, and Scattered Spider continue to refine their operations. Many campaigns are multi-stage and collaborative, with Initial Access Brokers providing footholds that are later sold to ransomware operators. One common thread is a focus on identity and infrastructure abuse – attackers are compromising vSphere environments, exploiting misconfigurations in third-party platforms, and abusing legitimate remote access tools to move laterally before launching extortion phases.
These incidents increasingly target complex organizations with sprawling digital footprints. The result? Weeks of operational downtime, lost revenue, regulatory scrutiny, and enduring brand damage. In this landscape, ransomware is no longer just a malware problem – it’s a business continuity issue, a supply chain risk, and a board-level concern.
The offense is automated: AI goes to work
This year, we saw AI break through hype and land firmly in attackers’ toolkits. Tools like WormGPT, FraudGPT, and DarkBERT gave cybercriminals an entry point to generate convincing phishing emails, polymorphic malware, and credential-harvesting scripts, all without needing advanced coding skills.
In our AI Offense blog, we detailed how these tools lower the barrier to entry and amplify the volume and sophistication of social engineering campaigns. Pair that with deepfakes, cloned voices, and LLM-powered targeting, and security teams now face threats that are faster, cheaper, and harder to detect than ever before.
The takeaway? AI is not a future threat. It is here. And defenders must embrace its potential just as aggressively as attackers have.
The human factor: Still the weakest link
Despite improved tooling, attacker playbooks still rely heavily on people. Our recent exploration of evolving social engineering trends highlighted the rise of Microsoft Teams-based impersonation, remote access tool abuse such as Quick Assist, and multi-stage credential compromise.
The fallout has been widespread. From attacks on major UK retailers to multiple airline disruptions and critical public sector breaches, social engineering is no longer just email phishing. It is phone calls, voice cloning, fake calendars, and chat-based manipulation.
Training helps. But attackers are innovating faster than awareness campaigns can keep up. Security teams need to simulate these threats internally and invest in visibility across identity platforms, because credentials remain the crown jewels.
From awareness to action: Resilience as a mandate
A growing number of incidents in 2025 underscored the readiness gap in many organizations. Our recent blog on preparedness broke down the UK’s National Cyber Security Centre guidance urging companies to revisit their offline contingency planning, including printed IR protocols and analog communications in case digital systems are taken offline.
This call followed a sharp rise in high-impact events, with over 200 nationally significant cyber incidents recorded in the UK alone this year.
The lesson? Cyber resilience is not a nice to have. It is foundational. Detection, backup, and patching are essential, but so is building response plans that assume failure, simulate outages, and bring the entire business to the table.
Join us: Predicting what’s next in 2026
We’ll explore these trends and where they’re heading in much greater depth in our Security Predictions for 2026 webinar, taking place on December 10.
Rapid7’s experts will unpack:
Which attacker tactics are here to stay and which are on the rise
Where AI, regulation, and infrastructure gaps are creating new exposures
How defenders can better prioritise risk and operate in resource-constrained environments
What CISOs, SOC leaders, and engineers need to align on in 2026 to stay ahead
This is our biggest global webinar of the year, and it is designed to help security professionals at every level get proactive and stay ahead of what’s next.
Register now and join thousands of security professionals from around the world as we set the stage for 2026. Because when the threat landscape keeps shifting, your best defense is a head start.
In this second installment of our two-part series on the construction industry, Rapid7 is looking at the specific threat ransomware poses, why the industry is particularly vulnerable, and ways in which threat actors exploit its weaknesses to great effect. You can catch up on the first part here: Initial Access, Supply Chain, and the Internet of Things.
Ransomware and the construction industry
The construction sector is increasingly vulnerable to ransomware attacks in 2025 due to its complex ecosystem and distinctive operational challenges. Construction projects typically involve a web of contractors, subcontractors, suppliers, and consultants, collaborating through shared digital platforms and exchanging sensitive documents such as blueprints, contracts, and timelines.
While essential for project delivery, this interconnectedness creates numerous digital entry points that attackers can exploit, mainly as many firms rely on outdated software and insufficient cybersecurity protocols. Adding to the challenge, construction companies often operate under tight deadlines and financial constraints, leaving little room for prolonged IT outages or data recovery efforts.
Ransomware attackers take advantage of this urgency, knowing that even short disruptions can halt entire job sites, delay multimillion-dollar projects, and damage reputations, making companies more likely to pay ransoms quickly.
Compounding the problem, many construction organizations lack dedicated cybersecurity staff and robust employee training, making them susceptible to phishing, weak passwords, and other basic attack vectors, as we talked about in part one of this series. The sector’s dependency on third-party vendors, who may have weaker security, amplifies the risk by widening the potential attack surface.
Together, these factors make it difficult for construction firms to detect, prevent, and recover from ransomware incidents, leaving the industry facing financial losses, operational chaos, legal consequences, and growing pressure to modernize its approach to digital security.
⠀
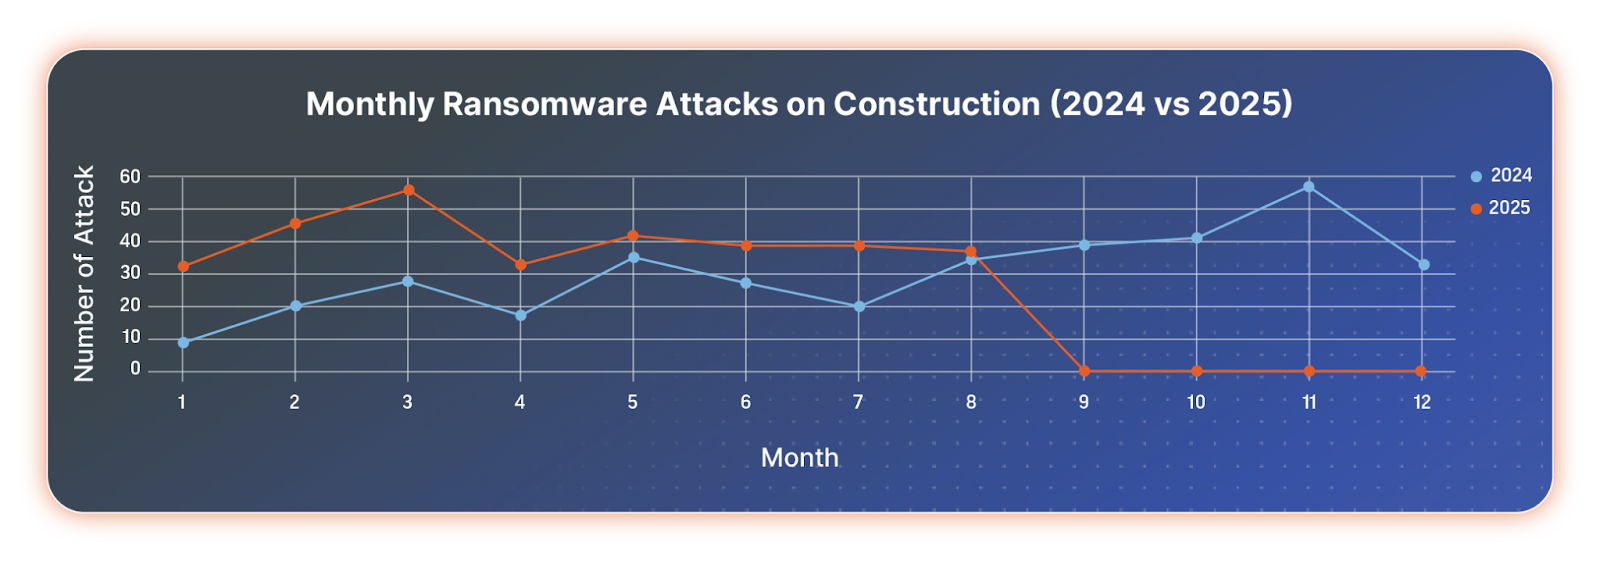
Monthly comparison of ransomware attacks against the construction industry 2024 vs. 2025
⠀
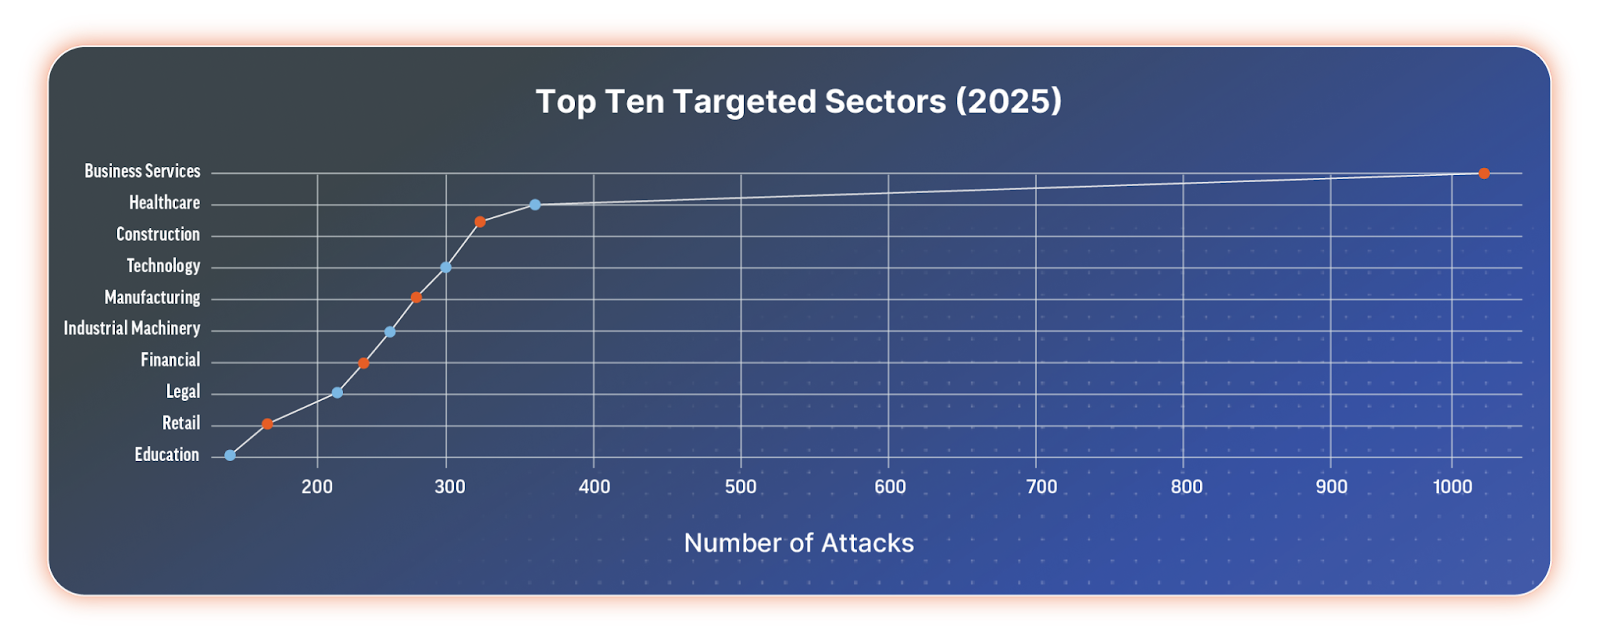
The construction industry is ranked among the top 3 most attacked sectors in 2025.
⠀
Top 10 targeted sectors in 2025
⠀
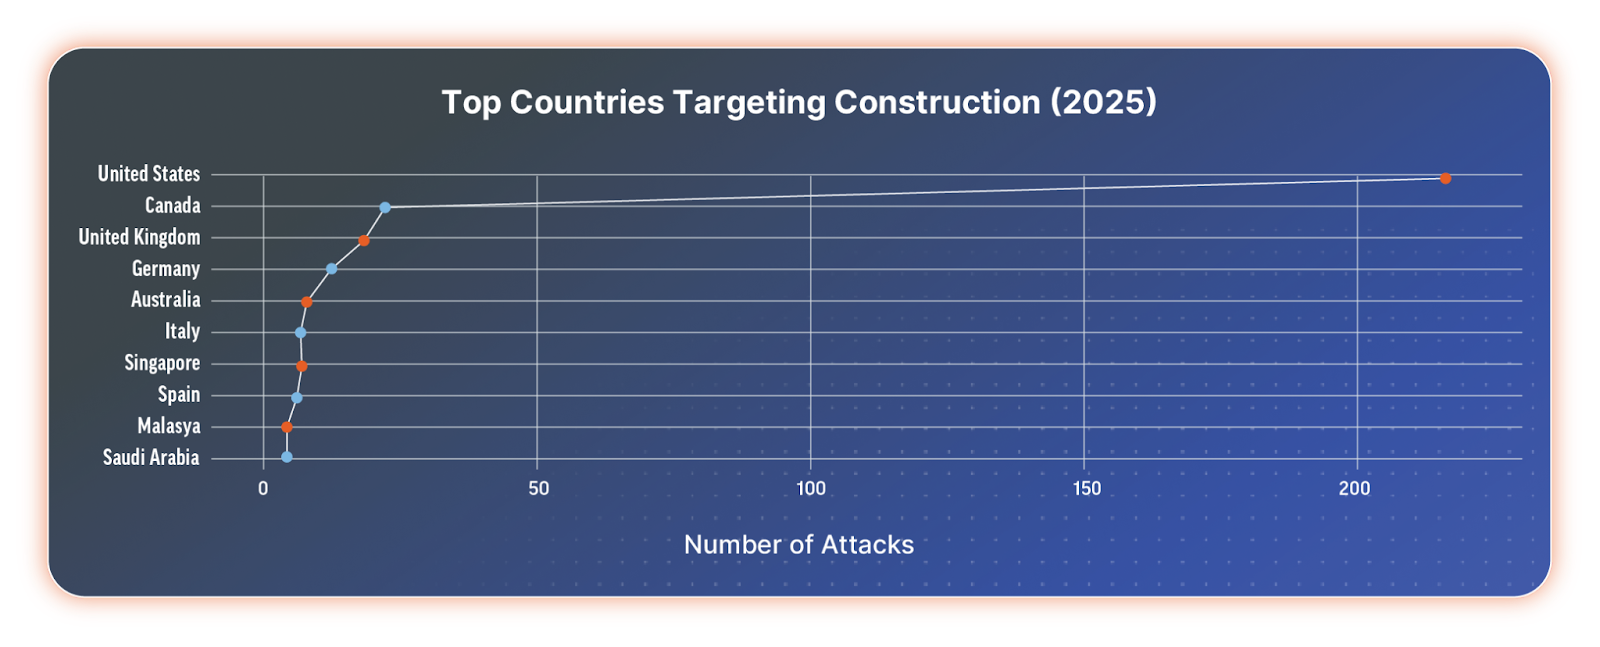
The majority of attacks are against companies in the United States, followed by Canada, the United Kingdom, and Germany.
⠀
Top 10 targeted countries in the construction industry in 2025
⠀
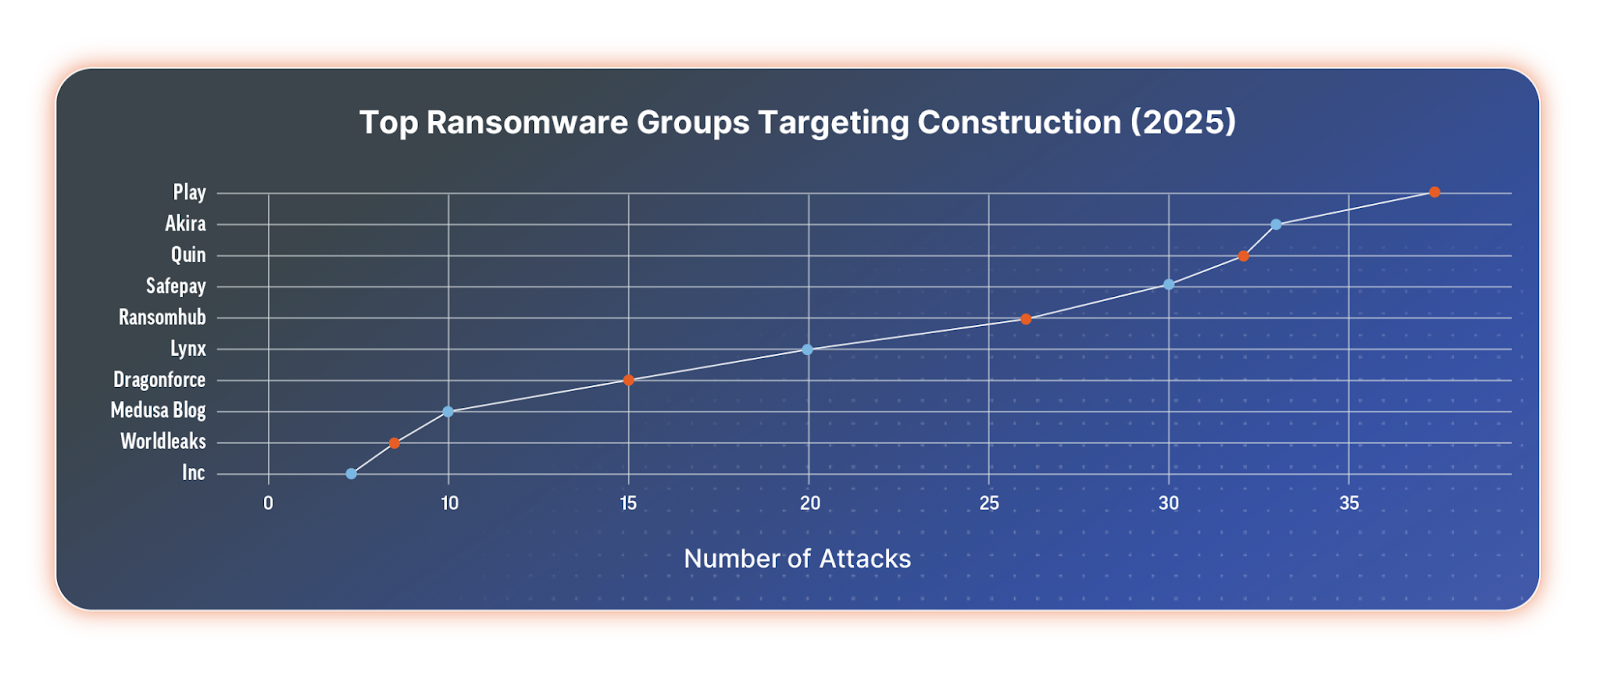
In 2025, the ransomware groups that targeted construction companies most frequently were Play, Akira, Qilin (AKA Agenda), SafePay, RansomHub, Lynx, DragonForce, Medusa, WorldLeaks, and INC Ransom. Notably, RansomHub is no longer active in its original form.
⠀
Top ransomware groups targeting the construction industry in 2025
⠀
Why the construction sector is attractive to ransomware groups
The reasons why ransomware groups have zeroed in on this sector are diverse and include the following:
High-value, time-sensitive projects
Construction projects are high-stakes endeavors, often involving multi-million (or even billion) dollar budgets and strict delivery deadlines. Even a brief disruption, whether caused by ransomware, data breaches, or system outages, can lead to costly project delays and penalties. Attackers know this, and they exploit the sector’s reliance on tight timelines to extort higher ransoms, banking on the urgency to restore operations.
Complex, interconnected supply chains
Few industries are as dependent on an intricate web of subcontractors, vendors, and service providers. Each connection in this sprawling supply chain presents a potential vulnerability. A compromised partner can serve as a gateway for attackers, enabling threats like supply chain attacks and lateral movement across multiple organizations. Securing every link is a significant challenge, especially when third-party cybersecurity practices vary widely.
Low cybersecurity maturity
While sectors like finance and healthcare have long invested in cybersecurity, many construction firms are only beginning their journey. Legacy systems, limited IT budgets, and a traditional focus on physical rather than digital risks have left gaps in defenses. As a result, attackers often find weaker security controls, outdated software, and unpatched systems, making this sector a prime target.
Accelerated digitalization and IoT adoption
Adopting cloud platforms, Building Information Modeling (BIM), IoT sensors, and smart machinery is revolutionizing project management and delivery. However, each new digital innovation adds to the attack surface. IoT devices, in particular, often lack robust security controls, providing attackers with novel entry points that are difficult to monitor and defend.
Exposure of sensitive intellectual property
Construction firms handle more than just blueprints. Proprietary architectural designs, bid documents, financial plans, and sensitive client data are all highly valuable and highly sought after by cybercriminals. The theft or exposure of this information can have devastating consequences, from reputational damage and loss of competitive advantage to implications for critical infrastructure and national security.
Commonly exploited vulnerabilities
Commonly exploited vulnerabilities by the above-mentioned ransomware groups include:
CVE-2025-31324 – The SAP NetWeaver Visual Composer file upload flaw. It enables unauthenticated threat actors to send specially crafted POST requests to the /developmentserver/metadatauploader endpoint, leading to unrestricted malicious file upload and full system compromise.
CVE-2024-21887 – The Ivanti Connect Secure and Policy Secure command injection flaw enables authenticated administrators to execute arbitrary commands on the appliances by sending specially crafted requests.
CVE-2024-21762 is a Fortinet FortiOS out-of-bounds write flaw that allows threat actors to gain super-admin privileges, bypassing the authentication mechanism, leading to remote code execution (RCE).
CVE-2024-55591 – The Fortinet FortiOS and FortiProxy authentication bypass flaw enables threat actors to remotely gain super-admin privileges by making malicious requests to the Node.js websocket module. Attackers were observed leveraging the flaw to create randomly generated admin or local users and add them to existing SSL VPN user groups or newly created ones. In addition, they add or modify firewall policies and other settings and log into the SSL VPN using these rogue accounts to allow network tunneling.
CVE-2024-40711 – The Veeam Backup and Replication deserialization flaw allows unauthenticated threat actors to initiate RCE.
CVE-2024-40766 – The SonicWall SonicOS and SSLVPN improper access control flaw. It enables unauthorized threat actors to access resources and, under certain conditions, cause firewall crashes.
What to do next
In 2025, the construction industry faces unprecedented digital opportunities and rising cyber risk. IoT, BIM, and cloud platforms have boosted efficiency but expanded attack surfaces, making firms vulnerable to ransomware, supply chain breaches, and IP theft. These risks, driven by fragmented supply chains, legacy systems, human error, and insecure devices, are systemic, not isolated. Cybersecurity must now be treated as a core pillar of project management, equal to safety, cost, and schedule, requiring board-level commitment and industry-wide collaboration.
To build resilience, firms should modernize legacy systems, secure supply chains, protect connected devices, and train all staff in cyber defense. Proactive measures like risk assessments, secure-by-design technologies, unified frameworks, and incident response playbooks must replace piecemeal defenses. By embedding security into daily operations and culture, the industry can turn cyber resilience into a competitive advantage, ensuring that innovation and protection move together to secure construction’s future.
The Q3 2025 Threat Landscape Report, authored by the Rapid7 Labs team, paints a clear picture of an environment where attackers are moving faster, working smarter, and using artificial intelligence to stay ahead of defenders. The findings reveal a threat landscape defined by speed, coordination, and innovation.⠀
The quarter showed how quickly exploitation now follows disclosure: Rapid7 observed newly reported vulnerabilities weaponized within days, if not hours, leaving organizations little time to patch before attackers struck. Critical business platforms and third-party integrations were frequent targets, as adversaries sought direct paths to disruption. Ransomware remained a most visible threat, but the nature of these operations continued to evolve.
Groups such as Qilin, Akira, and INC Ransom drove much of the activity, while others went quiet, rebranded, or merged into larger collectives. The overall number of active groups increased compared to the previous quarter, signaling renewed energy across the ransomware economy. Business services, manufacturing, and healthcare organizations were the most affected, with the majority of incidents occurring in North America.
Many newer actors opted for stealth, limiting public exposure by leaking fewer victim details, opting for “information-lite” screenshots in an effort to thwart law enforcement. Some established groups built alliances and shared infrastructure to expand reach such as Qilin extending its influence through partnerships with DragonForce and LockBit. Meanwhile, SafePay gained ground by running a fully in-house, hands-on model avoiding inter-party duelling and law enforcement. These trends show how ransomware has matured into a complex, service-based ecosystem.
Nation-state operations in Q3 favored persistence and stealth over disruption. Russian, Chinese, Iranian, and North Korean-linked groups maintained long-running campaigns. Many targeted identity systems, telecom networks, and supply chains. Rapid7’s telemetry showed these actors shrinking the window between disclosure and exploitation and relying on legitimate synchronization processes to remain hidden for months. The result: attacks that are harder to spot and even harder to contain.
Threat actors are fully operationalizing AI to enhance deception, automate intrusions, and evade detection. Generative tools now power realistic phishing, deepfake vishing, influence operations, and adaptive malware like LAMEHUG. This means the theoretical risk of AI has been fully operationalized. Defenders must now assume attackers are using these tools and techniques against them and not just supposing they are.
This is but a taste of the valuable threat information the report has to offer. In addition to deeper dives on the subjects above, the threat report includes analysis of some of the most common compromise vectors, new vulnerabilities and existing ones still favored by attackers, and, of course, our recommendations to safeguard against compromises across your entire attack surface.
Senator Ron Wyden has asked the Federal Trade Commission to investigate Microsoft over its continued use of the RC4 encryption algorithm. The letter talks about a hacker technique called Kerberoasting, that exploits the Kerberos authentication system.
Ransomware used to mean locked files and paralyzed systems. But today, bad actors are just as focused on exfiltration—the silent theft of sensitive data—and using that data as leverage for extortion.
According to cybersecurity firm BlackFog, 94% of successful cyberattacks in 2024 involved data exfiltration, either alongside or instead of encryption. Whether it’s stolen patient records, credentials, or source code, the goal is simple: Extract something valuable and threaten to leak it if demands aren’t met.
In this article, we examine how exfiltration became a leading tactic, the trends driving its rise, and what organizations—and cloud storage providers—can do to defend against it.
What is exfiltration?
In cybersecurity, exfiltration refers to the unauthorized transfer of data from a system—often done stealthily, and almost always with malicious intent. Think of it as the digital equivalent of corporate espionage: Data is copied, compressed, and quietly smuggled out. Unlike ransomware encryption, which slams the door in your face, exfiltration leaves the front door looking untouched.
The data being exfiltrated is rarely random. Cybercriminals are increasingly strategic about what they take and why. Common targets include:
User credentials
Personally identifiable information (PII)
Intellectual property and source code
Encryption keys
Shadow copies or backup snapshots
Tactics include exploiting cloud storage misconfigurations, hijacking legitimate credentials, or disguising traffic as everyday protocols like DNS or HTTPS. Increasingly, data exfiltration happens before the main event—laying the groundwork for extortion, credential stuffing, or resale on underground markets.
Recent cybersecurity trends related to exfiltration
Exfiltration has become the defining feature of modern cyberattacks, and the evidence is growing:
Double extortion is now standard. Threat actors exfiltrate data first, then deploy ransomware—or skip the encryption altogether—to maximize leverage. According to the 2023 Unit 42 Report, 70% of ransomware incidents involved data theft.
Infostealers, malicious programs designed to covertly harvest sensitive information, are on the rise. Over 2.1 billion credentials were stolen in 2024 alone, with malware like RedLine and Lumma making theft accessible to low-skilled attackers. While cybersecurity task forces (comprised of both government and enterprise actors) have made the news with high-profile disruptions of Lumma and other tools, the ability to use generative AI coding tools has meant that cyber attackers have a shortened time to deployment for malware tools.
Time to exfiltration is shrinking.Fortinet’s 2025 Threat Landscape Report notes that attackers can extract data in under five hours, while defenders often take days to respond.
Encrypted traffic masks malicious behavior. Emerging exfiltration techniques like QUIC-Exfil use modern, encrypted protocols to evade detection by traditional firewalls.
Together, these trends point to a world where stolen data is the main prize—and the threat doesn’t start when the ransom note arrives. It starts when your data quietly leaves the building.
Cloud misconfiguration and its role in exfiltration attacks
Exfiltration doesn’t always require malware—sometimes it only takes a misconfigured storage bucket or firewall rule. Cloud misconfigurations remain a leading cause of breaches, with public buckets, excessive identity and access management (IAM) privileges, and overly permissive network rules exposing data to the open internet.
Attackers exploit these gaps to quietly access or extract data without triggering alerts. A strong cloud posture management strategy—one that includes audit automation, implementing the principle of least privilege, and configuring features like Object Lock or Bucket Access Logs—is critical to reducing exposure.
Defending against exfiltration is a shared responsibility
As exfiltration becomes a primary threat, defense requires collaboration between cloud storage providers and their customers. Here’s how the most effective strategies work together.
Immutable backups and Object Lock
One of the strongest defenses is immutability. Backblaze B2’s Object Lock, for example, allows files to be written once and protected from modification, deletion, or encryption for a set period. Even if attackers compromise credentials, the data cannot be altered or removed.
Visibility and outlier detection
Cloud providers are investing in making advanced logging and behavioral analytics available to users to detect data theft in real time. Some examples of these types of features include:
Granular access logging with IP and user-level metadata.
Rate limiting and download caps to prevent mass theft.
Outlier detection powered by machine learning to catch subtle deviations from baseline activity.
Best practices for customers
Storage-layer defenses work best when paired with customer-side security controls:
Adopt zero trust architecture: Never assume implicit trust. Continuously validate users, devices, and behaviors.
Use MFA and least-privilege access: Lock down credentials, rotate them regularly, and minimize exposure.
Encrypt data at rest and in transit: Use strong encryption standards (AES-256, TLS 1.2+) and managed key systems.
Monitor for exfiltration indicators: Watch for abnormal traffic volumes, geographic anomalies, and unexpected protocol usage.
Run simulated breach drills: Test your team’s ability to detect and respond to stealthy data leaks.
Cloud storage companies can help provide critical security layers, but stopping exfiltration is ultimately a shared responsibility. Combining provider-level resilience with customer vigilance is the best path forward.
In a world of silent theft, vigilance is your best defense
Exfiltration isn’t just an add-on to ransomware. In this environment, locking the doors isn’t enough—You need to monitor the exits.
By combining immutable backups, smart logging, credential controls, and proactive monitoring, organizations can shift from passive victims to active defenders. The best defenses today aren’t just about blocking access; they’re about knowing what’s leaving and making sure it can’t be used against you.
There has been a significant decrease in social engineering attacks linked to the Black Basta ransomware group since late December 2024. This lapse also included the leaked Black Basta chat logs in February 2025, indicating internal conflict within the group. Despite this, Rapid7 has observed sustained social engineering attacks. Evidence now suggests that BlackSuit affiliates have either adopted Black Basta’s strategy or absorbed members of the group. The developer(s) of a previously identified Java malware family, distributed during social engineering attacks, have now been assessed as likely initial access brokers, having potentially provided historical access for Black Basta and/or FIN7 affiliates.
Figure 1. Confirmed malicious chat requests, Feb 12 through May 7, as observed by Rapid7.
Overview
The first stage of the attack remains the same. The operator will flood targeted users with a high volume of emails, to the order of thousands per hour. This is often accomplished by signing the target user’s email up to many different publicly available mailing lists at once, effectively creating a denial of service attack when each service sends a welcome email. This technique is commonly known as an email bomb.
Following the email bomb, the strategy then splits between operators, though they all ultimately reach out to impacted users pretending to be a member of the targeted organization’s help desk. The majority of operators still perform this step via Microsoft Teams using either a default Azure/Entra tenant (i.e., email account ends with onmicrosoft[.]com) or their own custom domain. In rare cases however, operators, particularly those affiliated with BlackSuit, may forgo Microsoft Teams in favor of calling the targeted users directly with a spoofed number. This strategy, if successful, allows them to circumvent the cloud logging that would be recorded otherwise. For the first time, an explanation of the process written by Black Basta’s leader is also available for a summary of the process, in the context of explaining the attack to a new affiliate:
If the affiliate is able to gain the user’s confidence, they will still primarily attempt to gain access to the user’s asset — and thereby the corporate network — via Quick Assist. Quick Assist is a built-in Windows utility that allows a user to easily grant remote access to their computer to a third party. The utility has been widely abused for social engineering attacks, a trend which continues. BlackSuit affiliates in particular may also direct the user to a malicious domain that hosts a fake Quick Assist login page, for the purpose of harvesting their credentials.
Figure 3. Fake Quick Assist login page, functions as a credential harvester.
In cases where the affiliate is unable to get Quick Assist to work, they will still cycle through a variety of other popular remote access tools (e.g., AnyDesk, ScreenConnect), and if that still doesn’t work, they may simply hang up on the user and move on to the next target.
Figure 4. One of Black Basta’s operators discusses their strategy regarding remote access tools.
Black Basta had at least one caller template/script for this purpose:
Quickly obtaining reliable access to the target network is still the top priority in the early stages of the attack, typically facilitated by stealing the targeted user’s credentials. In the past this has been achieved, for example, via a QR code sent to the target user via Microsoft Teams or the download and execution of malware which creates a fake Windows authentication prompt.
Figure 6. One of Black Basta’s operators discusses the usage of QR codes for credential harvesting.
In some cases the operator who makes the initial call may also coerce the target user to provide an MFA code while still on the phone. Historically, operators will also attempt to steal VPN configuration files once remote access is established, which can allow them to authenticate directly to the network if the compromised user account is not remediated.
Figure 7. One of Black Basta’s operators discusses using stolen credentials to authenticate directly to the VPN for the targeted environment.
After the affiliate has successfully gained access they will typically transfer and execute malware on the compromised system. The specific malware differs per operator and typically marks the stage in which the access is passed from the caller to an operator within the group who specializes in what they refer to as “pentesting.” To facilitate the access, the operator who calls typically coordinates with the “pentester” to increase the chances of success. At this point in the attack the affiliate who called the user has already hung up under the guise of having fixed the spam problem, and the “pentester” then begins to enumerate the environment. Rapid7 has observed AS-REP and Kerberoasting attacks to be commonly attempted along with Active Directory Certificate Services (ADCS) abuse and other types of brute force password attacks.
Technical Analysis
After initial access has been achieved, the follow-on malware payloads that are downloaded to the compromised system and executed differ, per operator.
Java RAT
A large volume of social engineering incidents handled by Rapid7 have resulted in a Java RAT being downloaded and executed. This tactic was first observed by Rapid7 during October of 2024, and initially reported on in December 2024 in relation to the payload identity.jar. The first samples of the Java RAT observed by Rapid7 only utilized Microsoft OneDrive with optional proxy servers (e.g., SOCKS5) for a more direct C2 connection. The configuration was left in plain text, and did not contain any functionality to dynamically update or encrypt the configuration, primarily functioning only as a RAT via PowerShell session commands.
In the past 6+ months, development of the Java malware payload has continued to add/change numerous features. The Java malware now abuses cloud-based file hosting services provided by both Google and Microsoft to proxy commands through the respective cloud service provider’s (CSP) servers. Over time, the malware developer has shifted away from direct proxy connections (i.e., the config option is left blank or not present), towards OneDrive and Google Sheets, and most recently, towards simply using Google Drive. The logic of the RAT is obfuscated using various types of junk code, control flow obfuscation, and string obfuscation in an attempt to impede analysis.
Figure 8. Obfuscated logic within the Java RAT, where three simple statements become dozens of lines and indentations.
The Java RAT and other payloads are distributed within an archive, the link for which is most often sent to the target user via a pastebin[.]com link. In cases as recent as May of 2025, Rapid7 has observed that the archives are still being publicly hosted on potentially compromised SharePoint instances. The archive and the payloads within are named to fit the initial social engineering lure. For example, in a recent incident, the archive was named Email-Focus-Tool.zip, likely to help prevent suspicion by the targeted user during the attack. The archive contains a .jar file (the Java RAT), a copy of required JDK dependencies contained within a child folder, and at least one .lnk file intended to make the malware easy to execute.
Figure 9. The contents of an archive delivered by the threat actor and a `log.txt` file containing enumeration command output.
The archive is most often extracted to the staging directory C:\ProgramData\ prior to execution. In at least one case, Rapid7 has also observed the operator who initiated the attack outputting system enumeration data to a plaintext file in the same directory, a technique commonly used in the past by Black Basta. Historically, this is information that they share during the initial stages of the attack to assess the network and the type of defenses they may have to deal with. For example, shown above, the operator who initially accessed the compromised asset spawned a command prompt and redirected the output of the ipconfig /all and tasklist commands to the file log.txt.
Most recent versions of the Java RAT have the capability to use Google Sheets to dynamically update the stored C2 configuration, which includes a Google spreadsheet ID (SSID), proxy server IPv4 addresses, application credentials (OneDrive), and/or service account credentials (Google Drive). At least one of the Google Spreadsheets used in this way was observed by Rapid7 to have been taken down by Google, which highlights the potential unreliability of using certain cloud services as a malware traffic proxy.
Figure 10. A Google spreadsheet used by the malware for dynamic configuration updates was taken down by Google.
One of the first actions taken by the malware on launch is to check for an existing configuration in the user’s registry, and if it is not already present, the copy included within the .jar payload, contained within the file config.json, is written there. All samples analyzed by Rapid7 did not have debugging messages removed, allowing them to be viewed by simply executing the .jar file in a console window, as all the debugging messages are written to stdout.
Figure 11. Debug statement output after executing the Java RAT via console.
The registry value name(s) and content for the stored config are both base64 encoded (e.g., HKCU\SOFTWARE\FENokuuTCyVq\JJSUP0CEcUw9PENaNduhsA==), with the decoded configuration content being encrypted using AES-256-ECB. The encryption key is derived from a seed that is stored as a 16 byte string within a file named ek (encryption key), that is contained within the .jar archive. The registry key name, a randomized alphabetic string, is hard coded and stored in a similar manner within the file r_path (registry path). The malware creates a SHA256 hash of the encryption key seed string, and the first 32 bytes of the SHA256 hash are then used as the AES-256-ECB key to encrypt and decrypt the malware’s configuration. Every sample analyzed by Rapid7 contained a unique key seed, though a particular sample is often distributed (within the related archive) to multiple targets for an extended period of time, often around a couple weeks.
After checking and loading the configuration from the registry, local resource, or updated configuration, the RAT will then establish at least one PowerShell session.
Figure 12. Example process tree for the Java RAT.
The stdin and stdout for the PowerShell console are used to process remote commands. The commands sent to the Java RAT are proxied through the respective CSP by the malware creating two specific files within the cloud drive. The name of the files all contain the UUID of the infected asset, which is retrieved at the malware’s startup. There are two prefixes added onto the primary communication files, cf_ and rf_ which contextually appear to stand for create file and receive file, respectively. These two files correspond to the standard output (stdin) and standard input (stdin) of the PowerShell console. The malware uses the input file in two major ways. If the cf_ file (stdin) starts with a specific command string, the content following it will be processed by the malware to execute functionality implemented by the malware developer.
Figure 13. The logic for the `loginform` command within the if-else command processing chain used by the Java RAT. The malware developer did not update one of the debug statements for Google Drive.
Otherwise, the content will be executed as a regular PowerShell command.
Figure 14. The default case in the if-else chain executes the command string via PowerShell.Figure 15. The ‘execute()’ function within the same class executes the command string as a PowerShell command via jPowerShell.
Command
Function
send
Send a file from the operator’s machine to the infected machine.
recive
Upload a file from the infected machine to the relevant cloud drive. The command string includes a typo made by the developer.
extract
Extract a specified file archive.
loginform
Present a fake login prompt to the user. Entered credentials are validated locally, and if correct, are uploaded to the operator’s machine through the cloud drive. The username must be specified by the operator.
newconfig
Replace the existing configuration with one retrieved from Google Sheets.
checkconfig
Check Google Sheets using the SSID to see if an update is available.
startsocks5
Initiate a Socks5 proxy tunnel using python.
steal
Attempt to decrypt and steal stored browser database information. (e.g., credentials)
screen
Given a supplied URL, download and execute a Java class in memory.
Table 1. Command key for the Java RAT.
The previously seen credential harvesting payload, identity.jar, has now also been integrated into the Java RAT, and instead of writing the entered credentials to a randomly named file within the working directory, the RAT sends it to the cloud drive C2 file that has been designated to the compromised host. This functionality is executed by the operator by sending the loginform (the Java class is abbreviated as “Lf”) command to the RAT via the cloud drive file. After decompiling and deobfuscating the Java code that the module consists of, it can be cleaned up, recompiled, and executed as a standalone program. This allows us to see that the appearance of the module to the targeted user is the same, including the fake “Windows Security” title. A review of the code indicates that it has not changed in any other significant way. The harvester still forces the active window on top and will not let the user close the window without entering their password or forcibly terminating the process.
Figure 16. The credential harvesting window used by the Java RAT.
As a result of the cloud service credentials being stored within the malware payload, and that, for example, Google Drive stores a revision history for every created file by default, it is possible to view the entire history of commands sent to each infected asset, including stdin and stdout.
This gives a unique in console view of what the threat actor saw while they were hands-on-keyboard and executing commands. Command log snippets can be seen below, with identifying information redacted. Once access is established, the operator nearly always verifies the user’s name with the dir command and then uses this information to execute the loginform command, as the malware does not retrieve the executing user’s name on its own.
Infected Host GUID: 4C4C4544-0038-4610-8036-B6C04F394733 2025-04-24T16:53:34.038Z: dir c:\users\ 2025-04-24T16:54:47.967Z: loginform <username> 3 2025-04-24T18:40:36.584Z: net time 2025-04-24T18:42:54.426Z: whoami 2025-04-24T18:43:48.284Z: net user <username> /domain 2025-04-24T18:48:35.089Z: hostname 2025-04-24T18:49:57.182Z: net group "Domain Computers" /domain 2025-04-24T18:50:56.578Z: net time 2025-04-24T19:17:14.259Z: ipconfig /all 2025-04-24T19:19:44.442Z: hostname
Infected Host GUID: 594045B3-008B-4106-8FF4-B850DF6C76D0 2025-04-24T17:20:09.896Z: dir c:\users\ 2025-04-24T17:20:58.179Z: loginform <username> 3 2025-04-24T17:36:52.542Z: wmic qfe list brief 2025-04-24T17:40:13.454Z: net time 2025-04-24T17:41:26.860Z: ping -n 2 <domain_controller_hostname> 2025-04-24T17:49:08.598Z: net group "Domain Computers" /domain > c:\users\public\001.txt
In some cases, Rapid7 has observed a command log gap ranging from around 4 to 12 days, beginning after the RAT is successfully executed and the user’s credentials have been stolen. In some cases an SSH tunnel is also established before activity stops. This type of behavior indicates that the threat actor may not be intending to use the access for themselves, but rather sell it to another group that specializes in fully compromising the network towards various ends (e.g., data theft, extortion, ransomware). Rapid7 has also observed the access being used to test new malware payloads and functionality, rather than progress the compromise within the targeted networks.
Qemu
In a smaller volume of incidents handled by Rapid7, operators have been observed sending the user a Google Drive link to download a zip archive containing QEMU (Quick Emulator) and its dependencies, including a custom made .qcow2 (QEMU Copy-On-Write version 2) virtual disk image. The image contains a Windows 7 Ultimate virtual machine (VM) configured to automatically logon and execute a RunOnce registry key that launches a ScreenConnect installer. In most cases a link to a fake Quick Assist login page (credential harvester) was also delivered to the targeted user by proxy via a self-destructing link service such as 1ty[.]me alongside the Google Drive zip archive link.
Figure 17. Evidence left in the .qcow2 image, including a ScreenConnect installer, registry command, and QDoor malware.
Once the remote session is established in this way, the VM also contains a copy of QDoor, Rust malware that functions as a C2 proxy, which allows the the threat actors to tunnel C2 traffic through a proxy to the VM, on the infected machine in the target user’s environment. In all cases handled by Rapid7, the QEMU executable was renamed (e.g., w.exe/svvhost.exe), and, as the emulator of the VM, it is the source on the infected host machine for all network connections resulting from processes running inside the VM. QDoor malware has been attributed to the BlackSuit ransomware group by ConnectWise.
In more recent cases, Rapid7 has observed the BlackSuit affiliates distributing a much smaller (64MB vs. 8.6GB) .qcow2 image that contains TinyCore Linux. When the image is loaded by QEMU, the bootlocal[.]sh script that is executed upon startup of the TinyCore OS has been set by the threat actors to sleep unless a successful ping is made to one of their servers. Once the ping is successful, an ELF file, 123.out is executed which attempts to connect to a C2 server.
Figure 18. The contents of `bootlocal[.]sh within the TinyCore VM`
Within the command log of the VM image, .ash_history, a wget command is also present which indicates the external server that the 123.out file was originally downloaded to the VM from.
Figure 19. Part of the `.ash_history` command log within the TinyCore VM.
In an alternate tc.qcow2 payload observed by Rapid7, the TinyCore VM boot script will unconditionally execute two ELF files, nossl and ssl. These ELF payloads function as multi-threaded socks proxies, where the ssl copy uses the OpenSSL library to encrypt traffic and ssl sends traffic in plaintext. In both cases, the ELF payloads send registration information to the C2 proxy server on port 53, which is typically used for DNS.
Figure 20. The ELF `nossl` begins execution by setting the C2 IPv4 address. Debugging symbols were left inside the file, which shows the original variable names.Figure 21. The registration string sent by `nossl` to the C2 proxy server from within the TinyCore VM.
As shown below from the Black Basta chat leaks, BlackSuit has connections with the group, so the adaptation of their typical spear phishing attacks towards these types of social engineering attacks for initial access is unsurprising.
Figure 22. One of Black Basta’s operators (@tinker) discusses their connection to a member of the BlackSuit ransomware group, with Black Basta’s leader (@usernamegg).
Malware Testing
After migrating the Java RAT’s functionality primarily to Google Drive, the threat actor developing the malware also began including the service account they use to test the malware within their own lab environment. The most recent versions of the RAT now also have the command screen which can download and execute a new Java class in memory. The threat actor first tested this in their own lab before trying it in infected devices that they had gained access to, as seen in the command logs below. Despite the name of the command and the name of the Java class that the test payload has (Screenshot), the payloads have varying functionality, but are generally intended to dynamically add new functionality to the RAT. The first test payload observed loads the Java class Screenshot, which then downloads a shellcode blob via a hard coded URL, and injects it into a new java.exe process using the WINAPI calls VirtualAllocEx, WriteProcessMemory, and CreateRemoteThread.
Figure 23. Injection logic implemented by one version of the dynamically loaded Java Screenshot class.
The analyzed test shellcode payload would then perform local PE injection for an embedded Rust PE using NTAPI calls, which for the purposes of the test appears to only spawn a confirmation message box. The Rust PE has an original filename of testapp.exe, a PDB named testapp.pdb, and was originally compiled on 2025-04-10T15:45:28Z. Notably, the Rust PE did have the Windows Graphics Device Interface (GDI) library and several related function imports as dependencies, which could be used to access or manipulate the screen, but did not appear to be fully implemented yet.
Figure 24. Test message box spawned by the Rust executable `testapp.exe`.
The screen command was then successfully used several times in compromised environments, though for different reasons. In one case the operator simply used it as a way to check the external IP address of the infected host. The command log below shows the threat actor testing the screen command for the first recorded time, using the payload with the embedded Rust PE, within their lab, shortly before starting a new spamming/social engineering attack run (during which they would distribute several copies of the malware).
Figure 25. One version of the Java Screenshot class implements functionality to retrieve the infected host’s external IP address and save it to a file named `info.txt`.
Rapid7 observed at least one other Rust malware payload, updater.exe being used by the threat actor, which appeared to be a custom loader for the SSH utility, containing the PDB name rust_serverless_killer.pdb. As many of the compromises facilitated by the social engineering attacks have resulted in SSH reverse tunnels being established to provide access, the loader is likely an attempt to evade detections targeting SSH commands by obscuring the related metadata. The SSH executable being loaded has the same functionality however, and as a result the command line arguments that must be passed remain the same.
The threat actor tested a variety of functionality for the Java RAT within their test lab. This includes the zipped python RAT the group would historically upload, decompress and execute (facilitated by the built in send and extract commands), or distribute instead of the Java RAT. The python RAT has a similar command menu to that of the Java RAT. The python RAT has also been previously analyzed by Gdata with similar findings, who refer to it as Anubis (likely based on the source code) and attribute the malware to the FIN7 group.
Figure 26. The python RAT source labels the decrypted payload as “Anubis”.
InputStart@2025-03-28T13:31:01.430Z: checkconfig InputStart@2025-04-01T15:21:49.251Z: recive c:\programdata\video\log.txt InputStart@2025-04-03T17:01:26.653Z: send C:\Users\Public\Libraries\nature.zip extract C:\Users\Public\Libraries\nature.zip\qwerty dir c:\users\ InputStart@2025-03-28T14:01:17.825Z: checkconfig newconfig InputStart@2025-04-01T13:16:18.589Z: send C:\Users\Public\Libraries\nature.zip startsocks5 C:\Users\Public\Libraries\nature\debug.exe C:\Users\Public\Libraries\nature\test.py
Several commands executed in the threat actor’s test lab can be seen above, where the python based payload was delivered via the Java RAT. In several past incidents handled by Rapid7 the name of initial payload archives containing python malware was Cloud_Email_Switch.zip and the script was named conf.py, where the script was executed via a copy of pythonw.exe that had its metadata stripped. The threat actor appears to have now moved to using the Java RAT primarily instead of the python version, although the Java payload retains the functionality to upload, extract, and execute python scripts.
Command
Function
killexit
Immediately terminates the process.
ip
Creates a UDP socket targeting Google’s DNS server (8.8.8[.]8) and connects to it to retrieve the machine’s local IP address.
‘cd ‘
Change the working directory to one specified by the C2.
‘gt ‘
Steal a specified file or directory. Reads and sends the content straight to the C2. If the target is a directory, the script will archive it into a zip file first.
‘up ‘
Upload a file sent by the C2, to the infected host, to a specified file path.
env
If the C2 specifies a ‘list’ command, the RAT returns all the existing environmental variables. Otherwise returns a specific variable chosen by the C2.
!cf!
Create/update a key (named via hard coded string) in the user’s registry using configuration data sent by the C2. Allows for the malware’s configuration to be dynamically updated.
!tcf!
Test C2 addresses supplied by the current C2 in a new config, by creating a TCP socket to attempt to connect to the new address(es) supplied. Returns the result to current C2. Doesn’t update the config.
default
If one of the above commands is not present, create a child console process (cmd.exe) to execute the contents received from the C2 and return stdout.
Table 2. Command key for the python RAT.
Among the output of the commands the threat actor ran in their test lab, we can also see a listing of their Downloads directory. The output shows that they have likely been developing Rust malware since at least 2024-09-21. The test lab is most likely also the environment in which they compiled testapp.exe as Rust executables contain cargo references which include the user’s name, for example: C:\Users\User\.cargo\registry\src\<truncated>. In contrast, updater.exe, the Rust SSH loader previously mentioned, references the user lucak.
Figure 27. A listing of the Downloads directory on an asset within the malware developer’s test lab.
Finally, while setting up the testing environment, the threat actor made changes to several Google Drive files from what appears to be a personal Gmail account: palomo************[@]gmail[.]com. These changes were visible as numerous versions of the Java RAT were distributed with the threat actor’s test lab Google Drive service account credentials included.
Mitigation Guidance
Rapid7 recommends taking the following precautions to limit exposure to these types of attacks:
Restrict the ability for external users to contact users via Microsoft Teams to the greatest extent possible. This can be done for example by blocking all external domains or creating a white/black list. Microsoft Teams will allow all external requests by default. For more information, see this reference.
Standardize remote management tools within the environment. For unapproved tools, block known hashes and domains to prevent usage. Hash blocking can be done, for example, via Windows AppLocker or an endpoint protection solution.
Provide user awareness training regarding the social engineering campaign. Familiarize users with official help desk and support procedures to enable them to spot and report suspicious requests.
Standardize VPN access. Traffic from known low cost VPN solutions should be blocked at a firewall level if there is no business use case.
Require Multi-Factor Authentication (MFA) across the environment. Single factor authentication facilitates a large number of compromises. For example, If an attacker steals a user’s credentials and acquires the network’s VPN configuration, no MFA on the VPN allows them to easily access the environment.
Regularly update software and firmware. Ransomware groups like Black Basta are known to purchase exploits for initial access.
Rapid7 Customers
InsightIDR, Managed Detection and Response, and Managed Threat Complete customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on behavior related to this activity:
Detections
Suspicious Chat Request – Potential Social Engineering Attempt
Initial Access – Potential Social Engineering Session Initiated Following Chat Request
Attacker Technique – Base64 String Added to HKCU Registry Key
Suspicious Process – LNK Executes PowerShell via JAR
Suspicious Process – QEMU Loads Disk From Staging Directory
Credential Access – Steal or Forge Kerberos tickets
Anomaly Detection – Failed AS-REP Roasting Attack
Non-Approved Application – Remote Management and Monitoring (RMM) Tools
In the ever-evolving landscape of cyber threat actors, the lines between ideologically driven hacktivism and financially motivated cybercriminals have become increasingly blurred. Originally fueled by political, social, or ethical causes, hacktivist groups have historically engaged in digital protest through website defacements, data leaks, and distributed denial of service (DDoS) attacks.
However, in recent years, a noticeable trend has emerged. Some hacktivist groups are evolving into ransomware operations and even becoming ransomware affiliates. This transformation is driven by a mix of ideological fatigue, opportunity for financial gain, access to sophisticated tools, and the growing profitability of extortion-based attacks. The result is a new hybrid threat actor—one that merges the disruptive zeal of hacktivism with the ruthless efficiency of cybercrime.
Understanding this shift is crucial for defenders, as it represents a convergence of motives that complicates attribution, response, and mitigation strategies. To this end, we have examined three prominent examples of relevant threat actors, namely FunkSec, KillSec, and GhostSec, identifying the drivers behind their transition to financially motivated campaigns and exploring the shift in their modus operandi.
Threat actor analysis
FunkSec
The FunkSec ransomware group emerged within the cybercrime ecosystem as a rising star in December 2024. The ransomware-as-a-service (RaaS) group has claimed at least 172 victims to date. The group proudly promotes itself as an AI-driven ransomware group, with their encryptor, FunkLocker, and some of the malware’s source code allegedly generated using generative AI tools.
The group targets organizations from various sectors and regions, such as government, education, automotive, energy, IT, and manufacturing, located in countries like the United States, Israel, France, Italy, Germany, India, and Australia.
FunkSec started as a politically motivated hacking (hacktivist) group, specifically interested in targeting the United States (Figure 1). The group was known to be aligned with the “Free Palestine” movement (Figure 2), and associated itself with other hacktivist groups, such as Ghost Algeria and Cyb3r Fl00d. Among its affiliates are Scorpion (AKA DesertStorm, a suspected Algeria-based hacker), El_farado, XTN, Blako, and Bjorka (an alleged Indonesian hacktivist). In its early days, the group offered tools commonly associated with hacktivist activities, including services for DDoS and defacement attacks.
Figure 1 – FunkSec’s activities as a hacktivistFigure 2 – FunkSec’s statement against the USA and Israel
At some point, the group transitioned its focus from politically motivated attacks to a RaaS model, offering customizable tools to its affiliates. Its victimology also changed from government entities to organizations across various sectors, such as education, technology, telecommunications, and agriculture (Figure 3).
Figure 3 – FunkSec’s latest active DLS
FunkSec’s reliance on relatively simple malware development using AI-based tools also explains the fast transition of the group from targeted hacktivism campaigns to broader, financially-motivated activities, with a large number of victims in a short period of time (Figure 4).
Figure 4 – FunkSec’s victims on their DLS
The group’s transition has also been referenced on a Russian-speaking dark web forum, where the author mentioned a cybersecurity vendor’s article on FunkSec (Figure 5).
Figure 5 – FunkSec’s transition being referenced on a Russian-speaking dark web forum
KillSec
The KillSec hacktivist group (AKA Kill Security) has been active since at least 2021. The Russia-aligned group targets organizations from various sectors, such as government, finance, transportation, electronics, manufacturing, travel and recreation, retail, and consumer services, located in countries like India, Bangladesh, Romania, Poland, and Brazil. The group considers itself a “prominent hacktivist group operating in the cyber realm, with a focus on both disruption and digital activism.”
KillSec initially emerged as a hacktivist group aligned with the Anonymous collective, with its operations primarily including DDoS attacks and website defacements, before pivoting to ransomware operations in October 2023. KillSec’s ransomware variants, namely KillSecurity 2.0 and KillSecurity 3.0, are designed to encrypt files and demand ransom payments for decryption.
In June 2024, KillSec introduced a RaaS operation, advertising a locker for Windows environments written in C++ and a dashboard, enabling affiliates to observe detailed statistics, conduct chat communications, and customize ransomware configurations using a builder tool. In November 2024, the group launched an additional locker for ESXi environments, expanding the breadth of its operations (Figure 6).
Figure 6 – KillSec launches locker for ESXi environments
The group’s shift is aligned with the overall proliferation of RaaS programs, enabling less technically skilled individuals to conduct ransomware attacks with relative ease in exchange for a fee. The group has been advertising its RaaS offering in an attempt to attract cybercriminals and further broaden its affiliate network (Figure 7).
Figure 7 – KillSec looking for affiliates
Although in certain incidents, KillSec leveraged solely stolen data to extort the victims, the group appears to adopt mainly double extortion tactics, exfiltrating data in addition to encrypting it and demanding a ransom payment to prevent it from being leaked. The group operates an active dedicated leak site (DLS) to which it uploads the data of victims who refuse to pay the ransom. The group also uses its DLS to advertise its services, which include penetration testing, data gathering, and its RaaS program (Figure 8).
Figure 8 – KillSec’s services
It should be noted that KillSec’s DLS also features a “For Sale” section, offering data allegedly exfiltrated from the targeted companies for sale, with the prices ranging between $5,000 and $350,000 (Figure 9). The group likely introduced this section in an attempt to further monetize the exfiltrated data. This offering of stolen data and additional services further suggests the financially motivated nature of the group’s activity.
Figure 9 – “For Sale” section on KillSec’s DLS
GhostSec
The GhostSec hacktivist group (AKA Ghost Security, GhostSecMafia, and GSM) has been active since at least 2015. The Anonymous-affiliated group gained prominence with the #OpIsis and #OpParis campaigns, in which various hacktivist groups took down thousands of ISIS websites and social media accounts using defacement and DDoS attacks. Since then, GhostSec has participated in campaigns, such as #OpLebanon, #OpNigeria, #OpMyanmar, #OpEcuador, and #OpColombia. The group has also continuously launched cyberattacks on Israel in response to alleged war crimes, primarily defacing their websites to spread “Free Palestine” messages.
GhostSec’s shift towards financially motivated operations overlaps with the group’s collaboration with cybercriminals. In July 2023, GhostSec announced that they formed a partnership with the Stormous ransomware group to target organizations in Cuba (Figure 10). Following this announcement, Stormous and GhostSec jointly claimed extortion attacks against three Cuban government ministries, and GhostSec also expressed the potential for future joint operations against other countries. In August 2023, GhostSec, together with ThreatSec, Stormous, Blackforums, and SiegedSec, collectively formed a unified collective, naming themselves “The Five Families” (Figure 11). This collective attempted to extort the presidential website of Cuba and the Brazilian organization Alfa Comercial.
Figure 10 – Announcement of the alliance between GhostSec and Stormous on their Telegram channelFigure 11 – Announcement of the “Five Families” formation on their Telegram channel
GhostSec solidified its presence in the cybercriminal ecosystem with the launch of its RaaS program “GhostLocker” in October 2023, which was shortly followed by the release of its infostealer tool, GhostStealer (Figure 12). In January 2024, the updated “REWRITE” (aka GhostLocker 2.0) version of GhostLocker was released, with a fully featured management panel allowing affiliates to track campaigns and payouts. The threat actor promoted its malware-as-a-service (MaaS) tools heavily on its Telegram channels, demonstrating its intention to attract affiliates and, in turn, maximize its profits.
Figure 12 – GhostLocker’s release announcement
On May 15, 2024, GhostSec announced its retirement from cybercriminal activities and its return to hacktivism. The group stated that it reached this decision after having obtained enough funding to support its hacktivist operations. GhostSec further mentioned that Stormous would remain in charge of the management and operation of GhostLocker (Figure 13).
Figure 13 – GhostSec’s retirement from cybercriminal activities
It should be noted that Stormous seemingly had already incorporated GhostLocker into its operations, even before GhostSec’s retirement. As of May 2025, the group is still active and operates the Stormous RaaS program, which appears to be a continuation of GhostLocker. This development signifies the mutual assistance and influence among united threat groups, as collectives like the Five Families allow them to maximize the impact and breadth of their operations by sharing resources, audience, and knowledge.
Two sides of the same coin?
This analysis shows that the threat actors in scope, FunkSec, KillSec, and GhostSec, have followed a similar trajectory, pivoting from politically motivated, disruptive campaigns to financial extortion. This transition is likely facilitated by the public availability of leaked ransomware builders, such as LockBit 3.0, which threat actors can leverage to develop their payloads.
The groups specifically appear to have adopted double extortion tactics, exfiltrating data from their victims and then encrypting it, in an attempt to pressure them to comply with their ransom demands. However, despite their seeming ability to conduct ransomware operations, these groups appear to lack the level of sophistication and specialization that characterize top-tier cybercriminal groups, such as Cl0p and LockBit, which are mentioned in the Rapid7 Q1 2025 ransomware report.
Interestingly enough, all three groups embraced RaaS as their business model while pivoting towards cybercrime. This evolution is aligned with the overall current status of the ransomware ecosystem, as RaaS programs have become increasingly more common. Such programs, demonstrating the financial nature of their activities, enable threat actors to maximize their profits by allowing affiliates to use their ransomware kit for a fee and a percentage of the collected ransom.
This transition of FunkSec, KillSec, and GhostSec has also affected and amplified the victimology of their operations. While these groups once operated as hacktivists that primarily targeted government entities, their scope of activities broadened significantly as they shifted to ransomware attacks. Along this process, their attacks shifted from targeted to opportunistic, against organizations of different sizes, operating in diverse sectors and geographies, that could be relatively easily compromised.
While all of these groups follow the pattern, shifting from hacktivism to cybercrime, and specifically financially motivated RaaS operations, the reason behind this transition remains unclear. As an exception, GhostSec appears to have embraced cybercrime in an attempt to gather funding for its hacktivist operations, according to its exit message. It should be noted that other threat actors, such as CyberVolk, have also launched RaaS programs to fund their operations, but these efforts remain scarce.
Finally, other hacktivist groups, such as Ikaruz Red Team and their affiliates, also operate ransomware, but they do so to cause disruption and make political statements. Thus, the scope of their operations differs from financial gain and is not comparable to that of the groups included in this analysis.
Conclusion
The evolution of FunkSec, KillSec, and GhostSec from hacktivist collectives to RaaS operations highlights a recent trend of a shift in motivations, driving cybercriminal behavior. Initially, these groups were propelled by political and ideological aims, targeting governments and organizations in alignment with their perceived causes. However, over time, their focus has clearly shifted towards financial gain, as evidenced by their adoption of RaaS models that prioritize profit over ideology. As cybercriminals adapt to “market demands,” it becomes clear that financial motivation has come to dominate their activities, leaving behind the ideological roots of their earlier campaigns.
IP addresses: 82[.]147[.]84[.]98, 77[.]91[.]77[.]187, 93[.]123[.]39[.]65
Rapid7 customers
InsightIDR and Managed Detection and Response (MDR) customers have existing detection coverage through Rapid7’s expansive library of detection rules. Below is a non-exhaustive list of detections that are deployed and will alert on behavior related to the FunkSec, KillSec, and GhostSec ransomware activity. We will also continue to iterate detections as new variants emerge, giving customers continuous detection without manual tuning:
Suspicious Process – Malicious Hash On Asset
While this specific detection directly covers malicious binaries linked to ransomware operations, customers also benefit from a comprehensive suite of detections that alert on post-exploitation behavior often observed prior to ransomware deployment. These include detections for lateral movement, privilege escalation, and suspicious persistence mechanisms, providing layered defense even when the specific ransomware payload is novel or obfuscated.
When several major UK organizations, including well-known retail brands, found themselves caught in a cyber attack earlier this year, it made headlines. But this incident wasn’t the first, and it won’t be the last. It reflects a growing trend where attackers exploit third-party vendors to breach multiple businesses through a single point of entry.
In one case, the compromise stemmed from a vulnerability in MOVEit Transfer, a widely used file transfer tool. Attackers exploited the flaw through Zellis, a payroll provider servicing organisations such as Boots, the Co-op, and parts of the NHS. From that single access point, they were able to exfiltrate sensitive employee data, including names, dates of birth, national insurance numbers, and in some cases, bank details. Some customer data was also affected, although not financial information.
This wasn’t just a breach. It was a blueprint—and a clear signal that even the most trusted brands are vulnerable when third-party risk is left unaddressed.
A back door into the business
The MOVEit vulnerability, first exposed in mid-2023, has become a favoured entry point for criminal groups looking to conduct high-volume, high-impact attacks. In this instance, attackers reportedly linked to the group Scattered Spider moved quickly, exploiting the flaw to access data at scale.
They didn’t need to phish credentials, crack passwords, or trick users. They found a vulnerable service buried in the supply chain and used automation and speed to do the rest.
This type of breach is becoming alarmingly common. Attackers increasingly target third-party software and services, i.e. vendors with connections to dozens or hundreds of organisations, because it maximises the potential return on effort. Instead of breaching one business at a time, they go upstream and compromise a shared dependency.
Scattered Spider in particular has shown a keen focus on the retail sector, where high transaction volumes, rich identity data, and complex supply chains create an attractive threat surface. As noted inDark Reading, these groups are playing the long game—building persistent access, quietly exfiltrating data, and returning to monetise later.
This is third-party risk in action. And it’s only becoming more sophisticated.
Modern threat actors, old-school outcomes
Rapid7’s threat intelligence teams have tracked how ransomware groups and data extortion crews have professionalised their operations over the past two years. These groups are no longer operating in the shadows. They’re mimicking enterprise structures, with revenue sharing models, support desks, marketing channels, and on-demand tooling.
Groups like DragonForce, for instance, use a white-label ransomware-as-a-service model built on LockBit code, offering affiliates a fully managed platform for launching attacks. As Raj Samani, SVP and Chief Scientist at Rapid7, noted in recent research, these groups provide their affiliates with everything they need to run sophisticated campaigns: prebuilt infrastructure, encryption tools, data leak sites, and communication channels. Their tactics often involve dual extortion – stealing data and threatening to publish it unless a ransom is paid, adding public pressure to the private pain of a breach.
This business-like approach is exactly why ransomware remains one of the most dominant threats in 2025. Ransomware today is less about disruption and more about strategy. Our recent analysis explores how these attacks have evolved from smash-and-grab to long-game economics, with extortion tactics designed to exert maximum pressure over time.
But the financial hit is only one part of the damage. As Raj explores in this piece for the Cyber Threat Alliance, the broader impact of cybercrime often goes uncounted—from reputational fallout and operational disruption to the long-term toll it takes on people and trust. These are the consequences organisations must now plan for, not just respond to.
These tactics are playing out across the retail sector and beyond. Attackers are using known exploits, moving efficiently, and causing maximum disruption—not by inventing new techniques, but by taking advantage of weaknesses businesses continue to overlook.
The visibility gap
The obvious takeaway is that third-party risk is real, and growing. But there’s a deeper issue beneath the surface: many organisations lack the visibility they need to see where their risk truly lies.
As we’ve argued before, proactive visibility is foundational to strong cybersecurity. If you don’t have a live, accurate view of your external exposure across infrastructure, vendors, applications, and user behaviour, you’re already behind. And if you don’t understand how your systems interact with those of your partners, you can’t realistically assess the blast radius of a third-party breach.
This is where a Continuous Threat Exposure Management (CTEM) approach is essential. CTEM isn’t about reacting to every vulnerability alert. It’s about identifying which exposures are most likely to be exploited and putting the processes in place to resolve them before attackers take advantage.
That means:
Mapping your external attack surface, including shadow assets and forgotten systems
Actively monitoring your vendors and data flows, not just annually but continuously
Understanding exploitability, not just vulnerability, to focus on risk, not noise
Running simulations, tabletops, and breach-and-attack testing to stress-test your response before the real thing hits
The goal isn’t perfection. It’s preparedness.
From theory to action
The real takeaway for security leaders isn’t “this could happen to us.” It’s the recognition that some version of this is already happening—whether they know it or not.
Attackers are scanning your environment. They’re probing your vendors. They’re replaying leaked credentials and looking for unpatched services. What they find, and how quickly you detect and respond defines the outcome.
This is why we encourage organisations to move from reactive defence to proactive control. You don’t need to boil the ocean. But you do need a plan that accounts for real-world attacker behaviour, not just compliance checklists.
At Rapid7, we advocate for a layered, risk-informed approach. That includes:
Exposure management that gives you live insight into where your business is vulnerable
Attack surface management that helps you find and fix weaknesses before they’re exploited
Managed detection and response (MDR) services that augment your team’s ability to act quickly and effectively
But more than any product or service, the most important element is mindset. Security is no longer something you install or outsource. It’s something you practice every day, across every level of the business.
Shared responsibility in a connected world
Breaches like this one also raise important questions for consumers.
As Rapid7 CTO EMEA Thom Langford recently pointed out, individuals can take practical steps to reduce their risk. That includes using a password manager to store strong, unique passwords, enabling multi-factor authentication (MFA), and avoiding the storage of card details in retail accounts. For frequent online shoppers, virtual or disposable cards offer an extra layer of protection.
Still, the burden cannot rest on individuals alone. Organisations must design systems that make secure choices the default. That means encrypting data at rest and in transit, enforcing MFA by default, and never storing sensitive credentials in plaintext.
In a hyper-connected digital economy, trust is everything. And trust is built through transparency, responsiveness, and consistent investment in security—even when there’s no breach in the headlines.
A final word
These attacks aren’t happening because a single business made a mistake. They’re happening because attackers are evolving and because the systems we all rely on are more interconnected than ever.
Security leaders can’t control every vendor or patch every flaw in someone else’s software. But they can control how they prepare, how they prioritise, and how they respond.
The organisations that come out stronger are the ones that treat security as a continuous discipline – one rooted in visibility, resilience, and readiness.
Because in 2025, the question isn’t whether you’ll be targeted.
In one of the most anticipated sessions of Take Command 2025, Raj Samani, Chief Scientist at Rapid7, sat down with Trent Teyema, former FBI Special Agent and President of CSG Strategies, for a candid conversation on how threat actors are evolving and what defenders must do to keep up.
Moderated by Brian Honan, CEO of BH Consulting, the panel pulled no punches. From the economics of ransomware to the risks of overrelying on static indicators of compromise, Inside the Mind of an Attacker: Navigating the Threat Horizon served as both a wake-up call and a roadmap for modern security strategy.
Cybercrime is thriving — and getting smarter
It’s no longer about lone hackers. As Raj put it, “Ransomware has become a business.” Today’s threat actors are highly organized, well-resourced, and increasingly leveraging professional tools and affiliate networks.
One striking takeaway: groups like RansomHub are reportedly earning tens of millions of dollars per quarter, reinvesting that revenue into toolkits, infrastructure, and even “customer service” operations for negotiating with victims.
Panelists discussed the trend toward secondary extortion tactics, where attackers threaten to notify regulators like the SEC if ransom demands aren’t met — a calculated move to increase pressure without deploying additional payloads.
From indicators to context: why threat intelligence must evolve
One of the biggest challenges facing defenders today is the lack of actionable, context-rich intelligence. While threat intel feeds are abundant, the signal-to-noise ratio is still too high.
“We don’t just need more data. We need better context,” Raj emphasized.
The panel discussed how defenders must move beyond static IOCs and invest in behavioral analysis, context-aware detection, and real-time telemetry to truly stay ahead of threats.
A recent stat from the post-event survey reflects this shift: only 18% of respondents said their organizations integrate threat intelligence into exposure management very effectively.
To beat an attacker, think like one
The message came through clearly: organizations that adopt a proactive, attacker-informed mindset are better equipped to defend against modern threats. That means:
Red teaming with real-world attacker playbooks
Understanding how ransomware operators stage and execute campaigns
Practicing lateral movement detection before it happens
Trent Teyema, drawing on his FBI experience, pointed out that too many organizations still rely on legacy thinking: “They treat cyber like IT, when they should be treating it like crime.”
Paying ransoms: a business risk, not a moral judgment
Both speakers addressed the uncomfortable reality: sometimes ransoms are paid. And while this remains a contentious topic, the panel framed it clearly – it’s a business decision, not a moral one.
Raj urged teams to have ransomware playbooks and decision frameworks defined in advance. This includes:
Knowing legal constraints (especially around sanctions and OFAC-listed entities)
Understanding the implications of payment
Engaging with experienced negotiation partners if needed
Visibility still reigns supreme
From attack surface awareness to SOC visibility gaps, the theme of visibility was woven throughout the session.
As Raj noted, “You can’t protect what you don’t know about.”
The panel closed with a call to action: unify your data, reduce siloed tools, and build detection and response around context, not just coverage.
Watch the full session on demand
If you missed this conversation — or want to rewatch it with your team — the full session is now available.
When was the last time you had a serious conversation about cybersecurity that didn’t touch on ransomware?
We all know that it’s one of the most persistent and damaging threats out there. Yet, this isn’t because it’s new—ransomware’s been around since 1989—but because we are making it far too easy for threat actors.
This year at RSA Conference, I gave a talk on why ransomware is still a thing in the year 2025. I explored key challenges, the rapid attack evolution, how the industry has responded, and whether today’s ransomware actors are truly innovating or just recycling old tricks.
Ransomware remains a crisis because we are still giving attackers the upper hand. To regain control, we need to understand how we’ve made it so easy for them, and what we can do to change that.
How did we get here? And why haven’t we stopped ransomware yet?
Cybersecurity investments continue to climb, with worldwide end-user spending on information security projected to reach $212 billion in 2025, according to Gartner. Still, the costs of cybercrime are continuing to escalate. With the FBI reporting a record $16.6 billion in losses in 2024 and identifying 67 new ransomware variants, it’s clear the threat landscape continues to thrive.
How is still this happening? With the steady increase in global law enforcement and legislative initiatives, as well as advancements in offensive and defensive technologies, shouldn’t progress be happening?
The fact is, attacks are escalating just as quickly. As defenders look to shift left, so do attackers who are probing earlier and adapting faster.
For example, stronger endpoint protection pushed attackers to target the network edge, exploiting vulnerabilities in firewalls, VPNs, file transfer solutions, and cloud infrastructure. The shift to multi-factor authentication (MFA) adoption was countered by attackers adjusting their social engineering to create MFA fatigue attacks. As early AI-powered threat detection improved security, ransomware groups adjusted their tactics to better blend into normal network traffic.
The economics of ransomware
Continued successes have enabled the underground cybercriminal economy to flourish and invest in even better tools and tactics. The more mature groups now run structured, professional operations that are reinvesting ransom payments into new exploits, tools, and personnel.
Successful groups like RansomHub are estimated to be pulling in more than $40m, with profits at around $12m after expenses and splitting with affiliates.
Leaked chat logs from ransomware groups such as Black Basta and Conti reveal that they often function like legitimate tech start-ups, complete with affiliate programs, customer support teams, and even bonuses for their top-performing operatives.
With six-figure sums being spent on exploits—leaked Black Basta chat logs confirmed the offer of an Ivanti zero-day for $200,000—attackers can acquire new tools faster than security teams can patch vulnerabilities. This constant reinvestment fuels an escalating cycle of attacks.
Established gangs are branching out into RaaS as a reliable money spinner, allowing lesser groups to launch attacks above their paygrade.
The more organizations are tempted by the ‘easy’ way out by paying up, the more capital threat groups have at their disposal. Big payouts also encourage gangs to hike up their ransom demands further. Meanwhile, paying is no guarantee of regaining stolen data—and attackers may return to exploit previous victims all over again.
But are ransomware groups truly innovating… or just lazy?
One of the biggest fears around ransomware gangs is the prospect of them bringing out advanced and unknown new attack tactics.
We certainly do see some top-tier gangs investing in cutting-edge techniques. These include branching out into new programming languages such as Rust, Go, and Nim to evade traditional detection methods and developing stronger encryption techniques to make data recovery more difficult.
Meanwhile, some groups are exploring firmware-based ransomware, embedding malware in UEFI/BIOS to evade detection. Conti chat logs confirm active research into these techniques. If adopted widely, these threats could eventually take ransomware to a new level.
While AI is a leading concern, it isn’t widespread in ransomware yet. Chiefly because the old methods are still working for the threat groups. However, attackers are using AI for social engineering, including phishing chatbots and deepfake scams.
So, certainly there is innovation in the field, at least at the top end. But when you start looking at the trends, it’s apparent that groups are usually doing just enough to stay ahead of their victims and aren’t typically experimenting the way the forefront of the legitimate tech sector does.
There are a lot of fields we aren’t really seeing them explore. For example, I’ve considered the potential around targeting chipsets in an attack. If you put some malicious code into the firmware controlling your operating system, I can load ransomware in the CPU and execute the ransomware from the chipset. There’s really no way for an antivirus tool to spot that before it activates during boot up. We’ll leave that there though for now—we don’t want to give them ideas…
Anyway, the fact is most threat groups prioritize efficiency over true innovation, and there are clear signs of groups cutting corners wherever possible. Groups such as LockBit and Conti have borrowed from REvil’s leaked source code instead of writing their own, for example. As the old saying goes, “if it ain’t broke…”
While groups have become more automated, they typically scale up existing operations rather than investing in new malware and tactics. Further, simple phishing attacks continue to do the trick in most cases. Why bother with advanced exploits and AI-powered campaigns if your target still isn’t using MFA?
Fighting ransomware starts with the fundamentals
A dozen years after attacks like CryptoLocker set the trend for modern ransomware, it remains a critical threat as attackers continue exploiting the same gaps repeatedly. Weak credentials, unpatched vulnerabilities, and poor incident response planning are all maintaining ransomware’s status as a reliable moneymaker.
Enterprises must get their fundamentals right to break the cycle of attacks.
Many firms still lack full visibility into their attack surface, for example. Security teams cannot effectively defend their organizations without comprehensive visibility of their systems and the ability to identify where to implement controls that prevent unauthorized access, privilege escalation, and lateral movement.
MFA, while highly effective, is often deployed and configured incorrectly and does not cover critical systems, especially edge technologies like SSL VPNs, firewalls, and cloud services.
Likewise, vulnerability patching is another critical area that is often not completed quickly or thoroughly enough, creating a wide window for attackers to use exploits before fixes are applied.
At first, addressing the prioritization issue can seem daunting. Out of the hundreds of vulnerabilities a business may face, where do they start? In these situations context is key, so a good place to start is by bringing together technologies and curated intelligence, which provide the necessary context to prioritize patching. If organizations can boost awareness of actively exploited vulnerabilities, and patch these proactively, then the overall risk they face will be lowered.
Beyond prevention, organizations need to test their response capabilities. Red team and tabletop exercises are essential to testing how well teams can detect, contain, and recover from an attack. Firms must develop response and data recovery strategies that do not rely on paying ransoms, removing the financial incentive behind groups carrying out attacks.
While a lot of companies have this down on paper, they may not have gone into enough depth for the real thing. What if an attack strikes and the main decision-maker is on vacation and they didn’t bring their cell to the beach? Who’s the replacement, what happens next? All these things need to be planned out and tested in detail.
So yes, ransomware is still a problem in 2025, and it will remain central to security discussions. However, the sophistication of this threat is not as daunting as it may seem. Threat actors are opportunists who cut corners and rely more on defenders making mistakes than their own skillsets.
To start winning this battle, organizations don’t need to take drastic measures. They need to get the basics right and take back control. No more giving the adversary easy wins.
AI is rewriting the rules of technology, for better or worse. Arguably one of the most “for better and worse” areas? Ransomware. It’s a full blown billion dollar business, and AI is supercharging both the offense and defense.
Not only are we seeing AI give bad actors more sophisticated tools and campaigns to target business and consumers alike, we’re also seeing mitigation techniques and technologies deployed by good actors gain equally compelling AI-powered improvements.
In other words, welcome to the future—where your data is the hostage and the bots are negotiating. Let’s dig in.
Some stage-setting: How much is ransomware costing us?
Despite ransomware payments exceeding an eye-watering $1 billion in 2023—and despite some high profile attacks in 2024, one of which extracted $75 million from a single victim—ransomware attacks actually fell overall in 2024. High profile law enforcement activity, like those against LockBit and BlackCat contributed to a huge drop in the second half of 2024.
Don’t get too excited though: According to cryptocurrency tracing firm Chainanalysis, that still meant $814 million in 2024. And, the true cost of ransomware includes more than just payments extracted under threat.
The economic ripple effects of a ransomware attack can include losing C-level talent, having to lay off employees, and ongoing downtime or business closure. Industry-wide, cyber insurance is a growing industry, and 2024 saw a staggering 31% of claims come from third-party risk.
Perhaps most concerningly, ransomware attackers are increasingly using exfiltration as a tactic to double and triple extortion, even using exfiltration data to launch targeted distributed denial-of-service (DDoS) attacks. According to a Check Point’s 2025 Cyber Security Report, some new actors have emerged as exclusively “data-selling platforms,” hosting dedicated data leak sites (DLS) and negotiation platforms.
The good news
Machine learning (ML) tools have underpinned modern cyber security techniques for years now—with excellent results.
Sophisticated monitoring tools give us far more granular insights and alerts.
AI-driven behavioral analysis is making it easier to detect anomalies and preempt attacks before they escalate.
What does this mean for defending against ransomware attacks?
Enterprises now have access to security platforms that analyze network behavior in real time, flagging unusual access patterns or lateral movement before a full ransomware payload can deploy. These platforms rely on machine learning models trained on massive datasets of known attack vectors, which allows them to flag and quarantine suspicious activity with impressive accuracy.
The interesting thing is that common knowledge says that “the AI revolution” has been happening recently, and quickly. But, when it comes to cybersecurity defense, many tools have been using ML algorithms for at least two decades. Palo Alto Networks (WildFire), for example, has been using ML since 2003.
The line between “processing massive datasets and acting up on that info based on programmed parameters” and machine learning is subtle, but important. While the former follows set parameters, machine learning identifies patterns in data—sometimes with human guidance—to decide from multiple possible actions.
It’s like teaching an assistant a series of tasks they can eventually do on their own. When you think about the progression from basic automation to ML, AI, and deep learning, the shift from rule-based actions to autonomous, chained decisions starts to make a lot of sense.
Zero trust architecture, enhanced by AI, is also gaining momentum. Instead of relying on perimeter-based defenses, AI-enhanced systems enforce granular access controls and continuously verify user and device trust levels. In practice, what this means is that systems no longer assume that you are you on the other end—not without evidence. Combine this with real-time threat intelligence sharing and automated incident response, and enterprises can shorten the window between detection and mitigation drastically.
The bad news
Deep fakes are more convincing.
The ability to generate code means there are more attacks, and those attacks are more sophisticated and responsive.
Cyber criminals of all skill levels have access to more technical tools, including some that are specialized in malware.
Enterprises are adjusting to a new way of working, which can create vulnerabilities.
Generative AI, phishing, and deep fakes
The low-hanging fruit in this discussion is that it’s easy to use generative AI to create more convincing phishing attacks. In the past, bad grammar or non-localized language choices have been an easy way to quickly identify a phishing attack.
Assisted by generative AI, deep fakes of both the voice and video flavor are getting increasingly difficult to spot—so, while you know your CEO isn’t likely to text you to get a bunch of gift cards or send them company funds via Bitcoin or PayPal, you might believe a video of your CFO or a call from your CEO asking you to transfer funds to accounts that turn out to not be legitimate.
How is generated code being used by ransomware bad actors?
Just as generative AI models have made everyone a poet, they’re also widely used to generate code. Tools like GitHub Copilot have seen wide adoption amongst enterprises looking to generate and test code. Gartner reports that by 2027, 70% of professional developers will use AI-powered coding tools, up from less than 10% in 2023.
Given how AI code generation has made code generation easier on enterprises, it’s no surprise that the ransomware industry is following the same adoption trends. By January 2023, this had gone from a hypothetical to a reality, with ransomware bad actors of low levels of technical skill able to leverage LLMs to create malware scripts.
By July 2023, cybercriminals were already discussing WormGPT, a malicious chatbot trained on ChatGPT which removed standard guardrails against creating illegal or inappropriate content. And, cybersecurity protection firms had executed a proof of concept to demonstrate that AI could generate truly polymorphic code on the fly—a technique used to make it much easier to evade detection by antivirus programs. By July 2024, one study showed that ChatGPT 4 was able to exploit 87% of one-day vulnerabilities.
Couple that with the fact that ransomware bad actors have opposite success metrics vs. enterprises. Cyber criminals rely on enacting as many attacks as possible, and it only takes one of those attacks succeeding to see a significant upside. Enterprises, on the other hand, only need one failure to see a huge negative impact on their businesses.
What things can you implement to be ransomware ready?
Some of these recommendations are things that users can do on every platform they interact with, such as:
Creating good, strong, unique passwords, and preferably using a password manager: A good password manager reduces password reuse and helps ensure best practices are followed enterprise-wide.
Enabling multifactor authentication (MFA): Multi-factor authentication remains one of the strongest lines of defense, especially when paired with device verification and biometric options.
On the enterprise side of the house, frameworks like cyber resilience help teams protect data they’ve been entrusted with. And, AI-powered cyber security tools can be a powerful tool in any business’s toolbox. That can look like a number of different things, including:
Investing in AI-powered endpoint detection and response (EDR). These tools continuously monitor and analyze endpoint activities, flagging unusual behavior and isolating threats automatically.
Training teams on recognizing deep fakes and AI-enhanced phishing attempts. Security awareness training is evolving fast. Focused, frequent, and AI-aware sessions are critical for employees across departments.
Leveraging deception technology. Deploying decoy systems, fake credentials, and honeypots can help trap attackers early and gather valuable intel on their tactics.
Running tabletop simulations. Practicing breach scenarios—especially those involving AI-enabled threats—prepares teams to act decisively when seconds matter.
Cyber resilience isn’t static, and neither are the tools and tactics. One of the most important areas an enterprise can invest in is ongoing security and research. Enterprise leaders need to prioritize proactive measures. That means ongoing AI model audits, being nimble in response to new and changing best practices, and investing in cross-functional teams that bring together infosec, legal, and operational leadership.
The future of AI and ransomware
Let’s level with each other—separately, the AI and ransomware spaces are both changing quickly. When you combine AI and ransomware and try to define how they’re affecting each other, you’re on pretty slippery ground.
What we’re trying to do here is identify patterns that affect our everyday lives—but we’re also taking a peek at what folks are studying in the research realm, because quantum is just around the corner, and, frankly, too impactful to ignore.
So, tell us if we need an update, or if you have another opinion! The comments section is open and we’re happy to chat.
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.