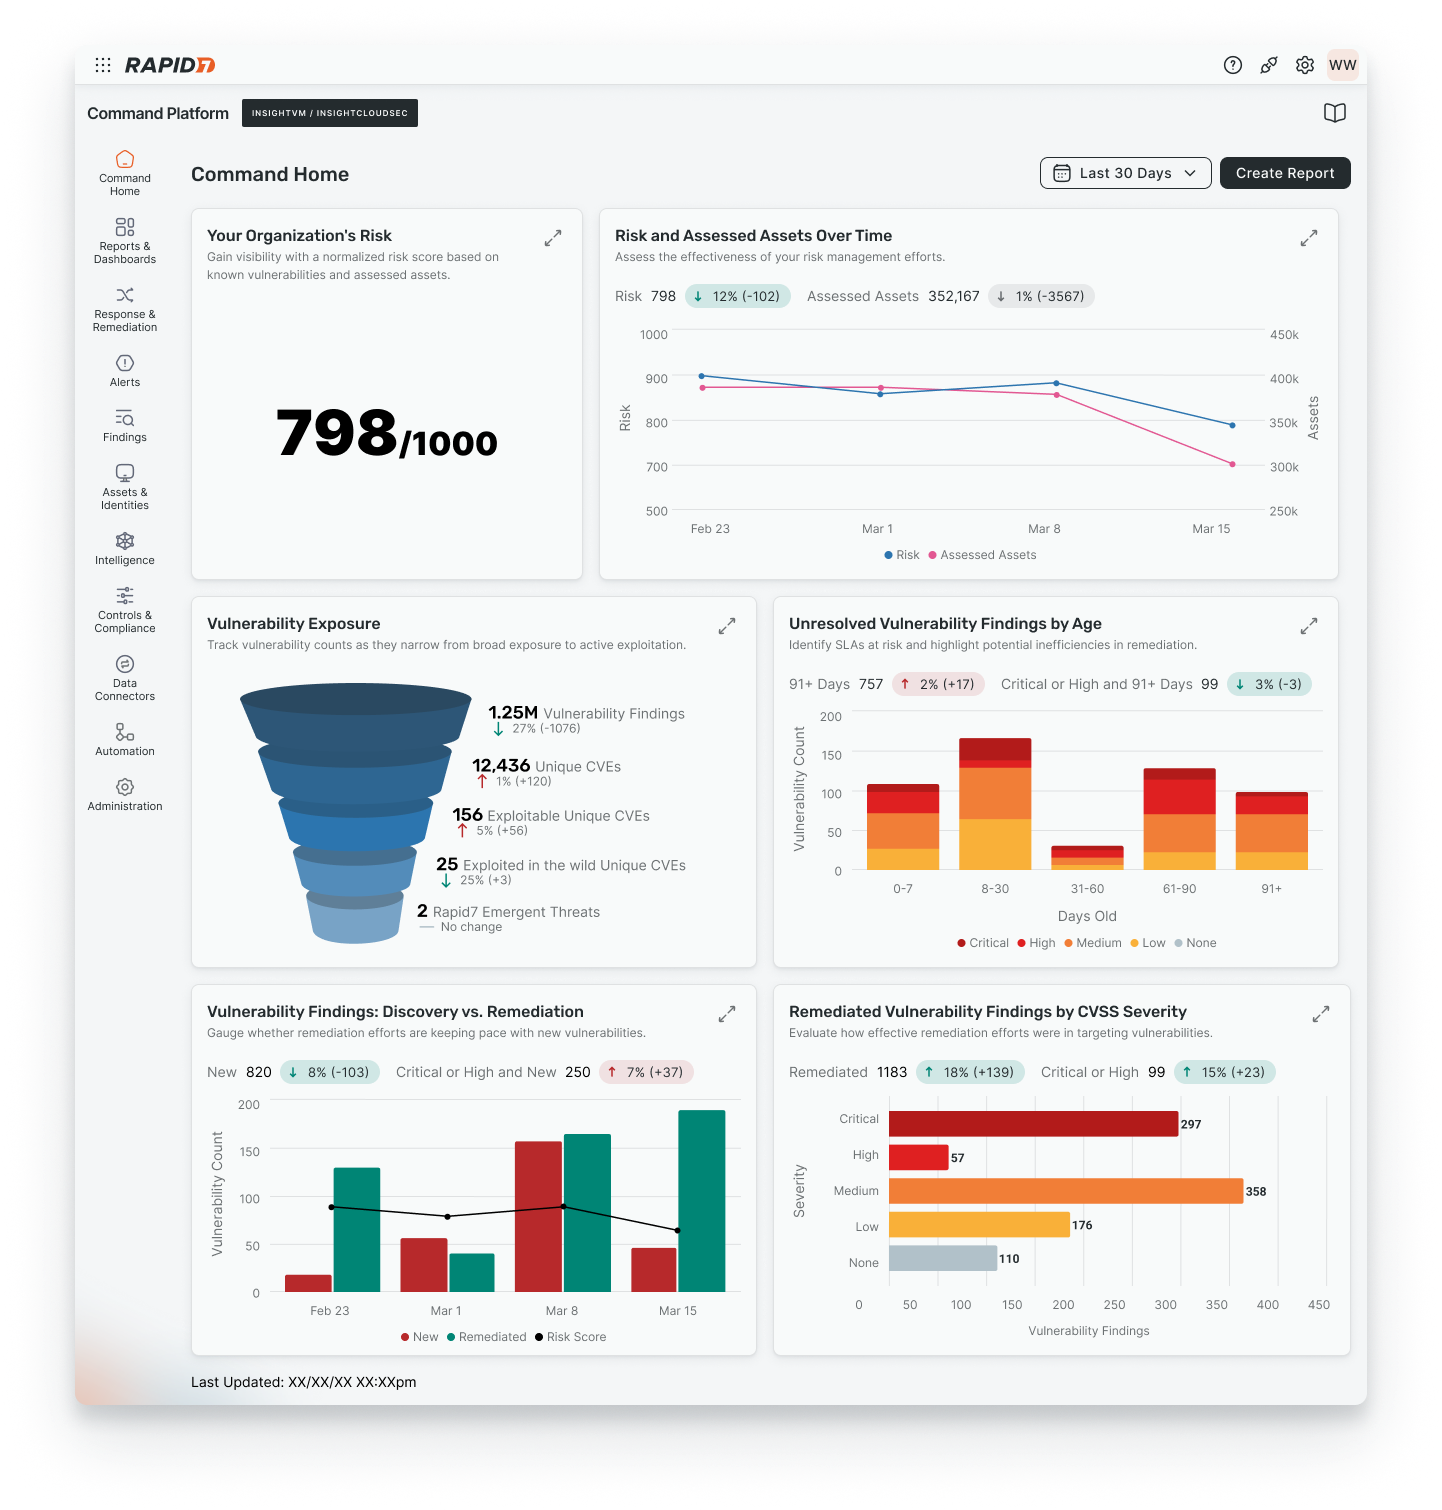
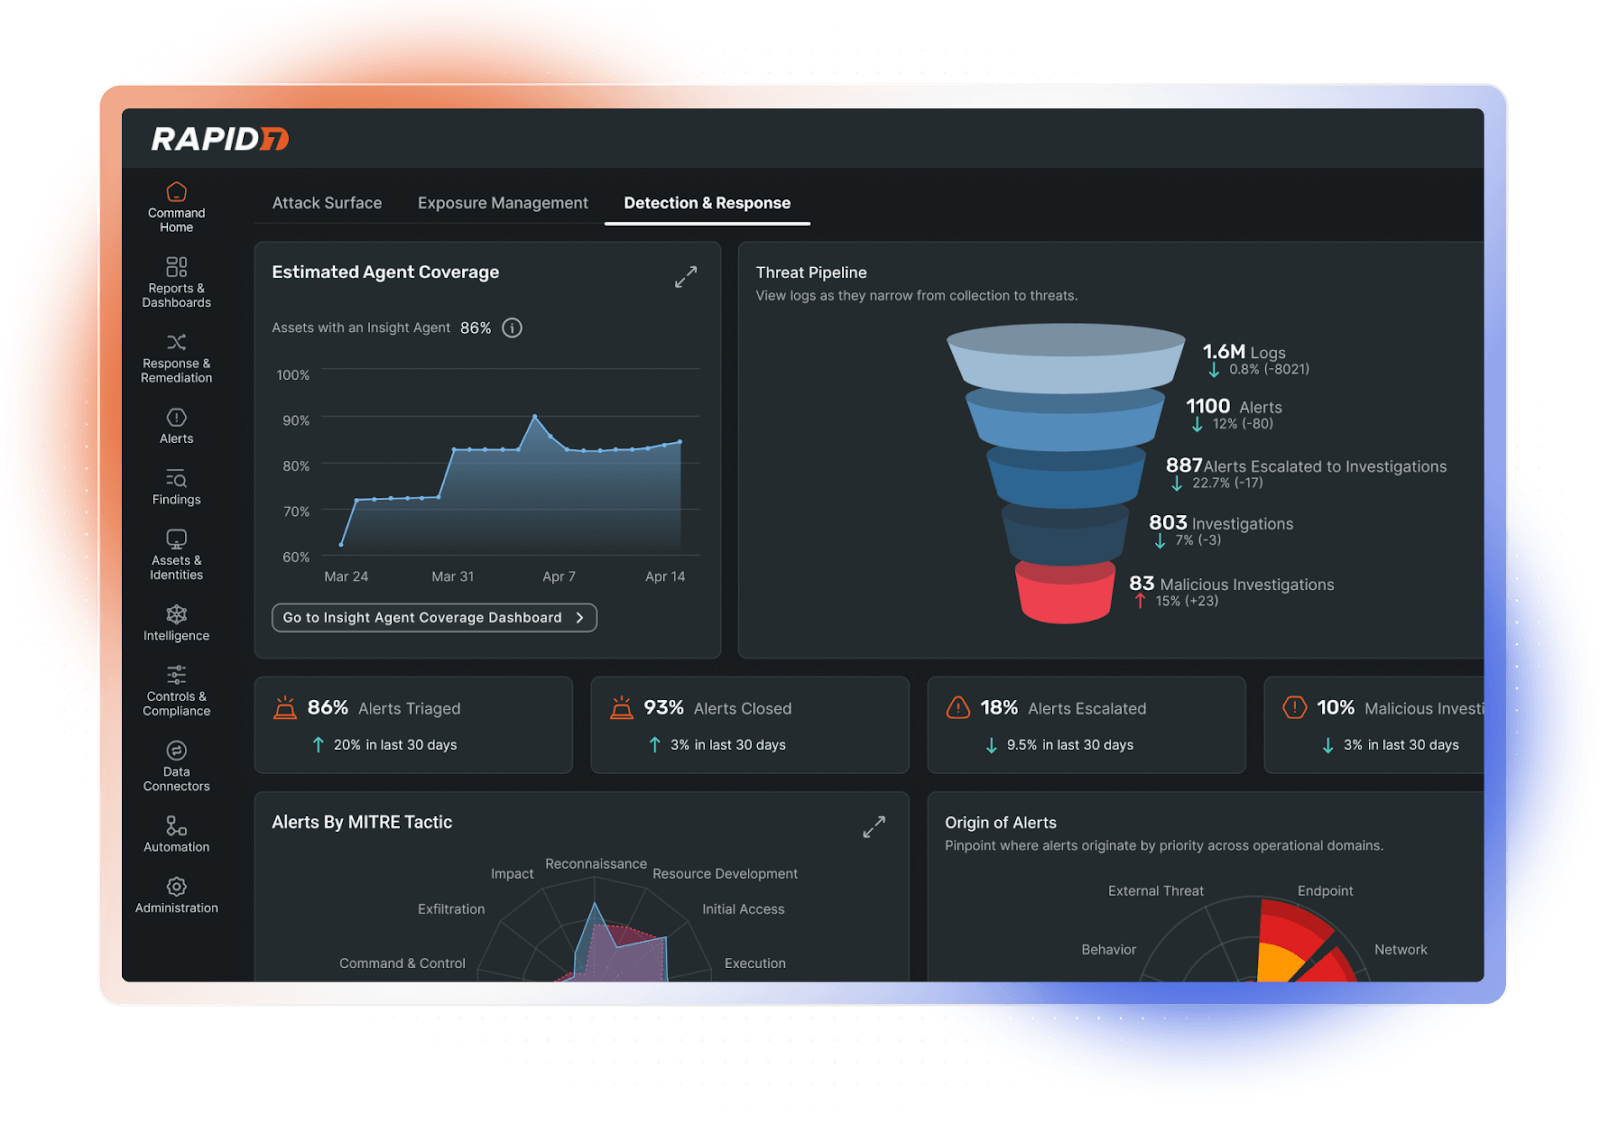
The managed detection and response (MDR) market has reached a turning point. We’ve gone beyond the baseline of 24/7 monitoring focusing on the speed of detection and moved to a world with a convergence of exposure management and response to deliver measurable, outcome-based defenses of a larger, AI-driven attack surface.
For anyone evaluating MDR right now, the Managed Detection and Response Services Landscape, Q3 2026 report by Forrester is a useful map that lays out where the market is heading. This is a market that has moved beyond “do you cover my telemetry?” to “Can a provider connect and prove that its activity is tied to real reduction in risk?”.
Rapid7 was named among the notable providers in this Forrester MDR Landscape. Being included matters to us, but the more interesting story is in what Forrester says about the market itself.
Detection and exposure are becoming one service
One of the report’s clearest signals is directional: Forrester writes that “MDR services will converge with exposure and posture improvement.”
That convergence is the whole basis of Rapid7 MDR and our Command Platform strategy. Most MDR services react after an attacker has already broken in. Rapid7 designed its service to anticipate where attackers are likely to succeed and disrupt them earlier. We combine exposure context, detection, and response into a single operational loop, where vulnerability findings and asset risk scoring flow directly into alerts and investigations. This means analysts can cut noise and focus response on the exposures most likely to cause business impact. It’s what we mean by exposure-informed, Preemptive MDR: The same context that tells you where you’re weak is the context that sharpens how you detect and respond.
For buyers, the practical implication is that old procurement habits are changing. Buyers used to invest in detection from one vendor, exposure management from another, and then hope the two solutions would seamlessly talk to each other. That approach is now turning into a liability.
The market will reward providers that connect these additions to measurable risk reduction rather than bolting on loosely joined SKUs. That’s a bar customers should hold every provider to, including Rapid7.
“Make providers prove the investigation, rather than narrate the dashboard”
The second theme is about accountability. In its guidance on working with providers, Forrester is blunt: Buyers should “make providers prove the investigation, rather than narrate the dashboard.” A slick activity feed is not evidence that anyone reached the right conclusion. Buyers should ask to see the reasoning behind a disposition, the actions taken, and the controls that keep automation from making unsafe decisions.
This is a healthy pressure on the whole market, and it’s a test we welcome. Rapid7 MDR is delivered on Rapid7’s own SIEM, which gives customers a direct window into our SOC, including validated threats, the response actions taken, where AI accelerated the work, and where a human analyst stepped in and why. Every action is logged, explainable, and auditable. As agentic AI takes on more of the investigation workload, that transparency becomes the difference between a service you trust and a black box you hope is working. Our approach is deliberately human-led and AI-enhanced: AI scales triage and investigation across large volumes of telemetry, while analysts stay responsible for validation and response decisions.
Accountability also shows up in commercial terms. Rapid7 MDR includes unlimited incident response, so the team stays engaged until an incident is fully remediated rather than stopping when a clock runs out, and gives a concrete answer to the “who owns the outcome?” question.
What to do with the report
If you’re evaluating MDR, and have access to Forrester, the report is a strong prompt to rewrite your evaluation criteria. A few questions worth taking into any provider conversation:
Ask how exposure context actually enters investigations. Is it a legitimate input to detection and prioritization, or a separate dashboard?
Ask to see a real, redacted case file rather than a metrics summary. Then probe how the provider handles uncertainty and model failure.
Clarify the place where accountability sits when a response action carries risk, and get a clear answer on how far the provider remains engaged during an incident.
These are the same standards we hold ourselves to, and they map to how we’ve built our MDR service. If you want to go deeper, our MDR Buyer’s Guide walks through what to look for in a partner, and you can compare Rapid7 MDR against other providers or talk to our SOC team directly.
The MDR market is one in which detection, exposure, and response stop being separate purchases and start being one accountable outcome. That’s the service we set out to build, and now is a good moment for every security leader to ask whether their current provider is heading the same way.
Source: Forrester, The Managed Detection And Response Services Landscape, Q3 2026, Jeff Pollard with Joseph Blankenship, Emily Doherty, and Michael Belden, September 1, 2026. Forrester does not endorse any company, product, brand, or service included in its research publications and does not advise any person to select the products or services of any company or brand based on the ratings included in such publications. Information is based on the best available resources. Opinions reflect judgment at the time and are subject to change. This report is part of a broader collection of Forrester resources, including interactive models, frameworks, tools, data, and access to analyst guidance. For more information, read about Forrester’s objectivity here .
IDC has named Rapid7 a Leader in the 2026 Worldwide Managed Detection and Response Service for Midmarket 2026 Vendor Assessment (Doc #US52992326, July 2026). We believe this recognition and research highlights where MDR is heading.
Many security programs are still built around a reactive sequence of detect, triage, and respond, but the timelines surrounding modern attacks have changed too quickly for that model to hold up on its own. Time-to-exploit has dropped from two years to 22 hours, while eCrime breakout time now sits at 29 minutes. In an environment like that, a program moving at human speed across siloed data, cannot keep pace. Rapid7’s view is that MDR must evolve accordingly, which is why we have been building toward a more preemptive security model.
What the IDC MarketScape said
The IDC MarketScape evaluation examined vendors across technical capability, service delivery, and strategic vision and two of IDC comments about Rapid7 stand out for us:
First, on how Rapid7’s MDR works differently:
“Rapid7’s Preemptive MDR model, which natively integrates vulnerability context, asset criticality, and attack path data directly into the analyst investigation workflow, provides a structurally differentiated detection approach that connects threat activity to underlying exposure in real time.”
This is the core of what we’ve built. Exposure management and detection and response work in our Command Platform’s unified data mesh, which means exposure context shapes what threats get surfaced, while active threat monitoring improves how exposure is prioritized. That connection is a meaningful part of how Rapid7 approaches MDR today.
Second, comments on threat intelligence:
“The combination of [Rapid7] Project Lorelei honeypot intelligence and Project Sonar internet-wide exposure data provides proprietary threat intelligence sources that are not replicated by other providers in the market.”
This threat intelligence is fueled by Rapid7 Labs, our dedicated global threat research and intelligence division, which constantly analyzes the global attack surface. Project Sonar catalogs public internet exposure, and Project Lorelei is our global network of honeypots that catches live attacker traffic. Together, they give Rapid7 a proprietary source of intelligence that feeds directly into detection engineering and investigation workflows.
Where MDR is heading next:
The recognition is important to us, but the more useful question is where MDR is heading and how Rapid7 is building for that shift. We are actively deploying autonomous AI agents in our Agentic SOC to handle the first hour of forensic investigation, including volatile memory collection, identity flow correlation, and initial triage before a human analyst opens the case. In practical terms, that is what responding at machine speed starts to look like inside a modern SOC.
Our MDR offering, Managed Threat Complete, includes unlimited incident response and a $1M Breach Protection Warranty, adding a stronger level of accountability for organizations that want MDR outcomes backed by both service depth and financial protection.
Read IDC’s full evaluation of Rapid7 here. If you’re evaluating your MDR approach, we’d like to show you what preemptive security could look like in your environment.
For years, security operations followed a familiar sequence: detect suspicious activity, investigate what happened, and respond before it caused significant harm. That model developed in a threat landscape where defenders had considerably more time to establish the facts and decide what to do next. In 2019, the average data breach took 206 days to identify and another 73 days to contain, creating a total breach lifecycle of 279 days.
As the time between initial access and attacker movement continues to contract, security teams are being asked to operate within a much narrower window. AI is accelerating reconnaissance, vulnerability discovery, and campaign execution, while defenders are responsible for growing volumes of data across cloud, identity, endpoint, SaaS, and AI environments, often without equivalent growth in analyst capacity.
Managed detection and response is evolving to meet those conditions by connecting exposure intelligence, machine-speed investigation, and human expertise. This approach helps security teams identify credible risks sooner, understand their potential impact, and intervene earlier in the attack lifecycle.
MDR must move beyond alert-driven investigations
When suspicious activity generates an alert, traditional MDR typically moves into investigation mode. Analysts gather information about the affected asset or identity, correlate activity across security tools, establish the scope of the incident, and determine the appropriate response.
Although each step is necessary, much of the initial work involves finding and organizing information rather than applying expert judgment. Analysts can spend valuable time collecting asset details, checking vulnerabilities, validating signals, and reconstructing context before the investigation can progress.
Recent research conducted with Omdia found that 93% of security leaders agree AI improves analyst efficiency by automating repetitive tasks. Giving machines responsibility for routine evidence gathering and correlation allows analysts to focus their time on complex investigations, business impact, and response decisions.
Preemptive MDR connects exposure and detection
Exposure management and security operations often provide different views of the same environment. Exposure teams understand which vulnerabilities, assets, identities, and attack paths present risk, while detection and response teams see activity as it unfolds. Connecting these views gives analysts more context at the beginning of an investigation.
Preemptive MDR brings asset criticality, internet exposure, vulnerability data, and threat intelligence directly into the SOC workflow. When an alert appears, analysts can immediately see why the affected asset matters, which weaknesses may be involved, and whether the activity aligns with known attacker behavior.
The same context can also support action before an alert fires. Intelligence indicating stolen credentials or compromised sessions can be surfaced before an attacker uses them, while newly disclosed vulnerabilities can be assessed against the organization’s assets and business priorities. MDR teams can then guide remediation towards the exposures most likely to create a viable route into the environment.
By moving exposure intelligence closer to detection and response, investigations begin with a clearer understanding of what is happening and where action will have the greatest effect.
Agentic SOC capabilities accelerate investigation
By bringing security data together across the environment, connected context creates the foundation for agentic SOC capabilities. Security investigations require evidence gathering, correlation, validation, and scoping, with many of these tasks repeated across every alert.
AI agents can perform elements of that work in parallel by examining telemetry, connecting related activity, testing possible explanations, and presenting analysts with a structured account of what happened, what is at risk, and which actions are available. Analysts can then review the evidence and apply their understanding of the organization, its priorities, and the potential consequences of a response.
While AI can accelerate much of the investigation process, human oversight remains essential to the way this model operates. The same Omdia research found that 92% of security leaders believe analysts should retain responsibility for final decisions, while 90% view human oversight as essential to the accuracy and reliability of AI-driven processes.² Agentic SOC capabilities can support that balance by accelerating repeatable investigation work while keeping analysts responsible for decisions that require judgment and accountability.
Connected security data strengthens AI-driven MDR
Because security AI can only work with the data and context available to it, the quality of that foundation has a direct impact on the investigation. An investigation is more useful when the system can connect an alert to the affected user, asset, vulnerability, cloud resource, and wider attack path without requiring an analyst to search across several tools.
Rapid7’s data mesh brings together asset, cloud, configuration, exposure, event, and alert data in a normalized layer. This gives AI-driven investigations access to connected security context at the point of analysis and helps reduce the manual work involved in reconstructing it.
From faster response to continuous defense
Bringing exposure intelligence, connected security data, AI-driven investigation, and human expertise into the same operating model creates a continuous defense loop. Exposure context helps teams identify where attackers are most likely to find an opening, detection reveals how those risks are being used in practice, and response reduces the opportunities available to the next attacker.
This approach allows MDR to contribute beyond the investigation of individual alerts. Each incident can improve future detection and prioritization, while exposure insights can guide action before suspicious activity develops into a larger event. Analysts gain the context to make better decisions, and automation gives them more time to focus on the threats and business risks that require their expertise.
The next evolution of MDR will be defined by how effectively providers connect these capabilities. By combining preemptive insight with machine-speed investigation and accountable human decision-making, security teams can act earlier, investigate faster, and continuously strengthen their defenses as the threat environment changes.
Rapid7 will showcase upcoming investments in Preemptive MDR and Agentic SOC at Black Hat USA in Las Vegas, August 3–6, 2026.
If Q1 set the pace for Rapid7’s tools, Q2 accelerated it. This quarter brought a steady stream of product enhancements, platform investments, and customer-driven innovation across Rapid7’s portfolio. Each release was designed with a clear goal in mind: helping security teams reduce complexity while increasing speed, context, and confidence in their day-to-day operations. Here’s a closer look at what launched in Q2.
Detection and response
Streamline investigations with bidirectional and enriched Microsoft Defender alerts
Bidirectional synchronization and enriched alert context for Microsoft Defender is now generally available for SIEM and MDR customers, enabling security teams to automatically synchronize alert status between Rapid7’s SIEM and the Microsoft Defender console. With added process tree and user identity context, analysts can investigate threats more efficiently while reducing manual effort.
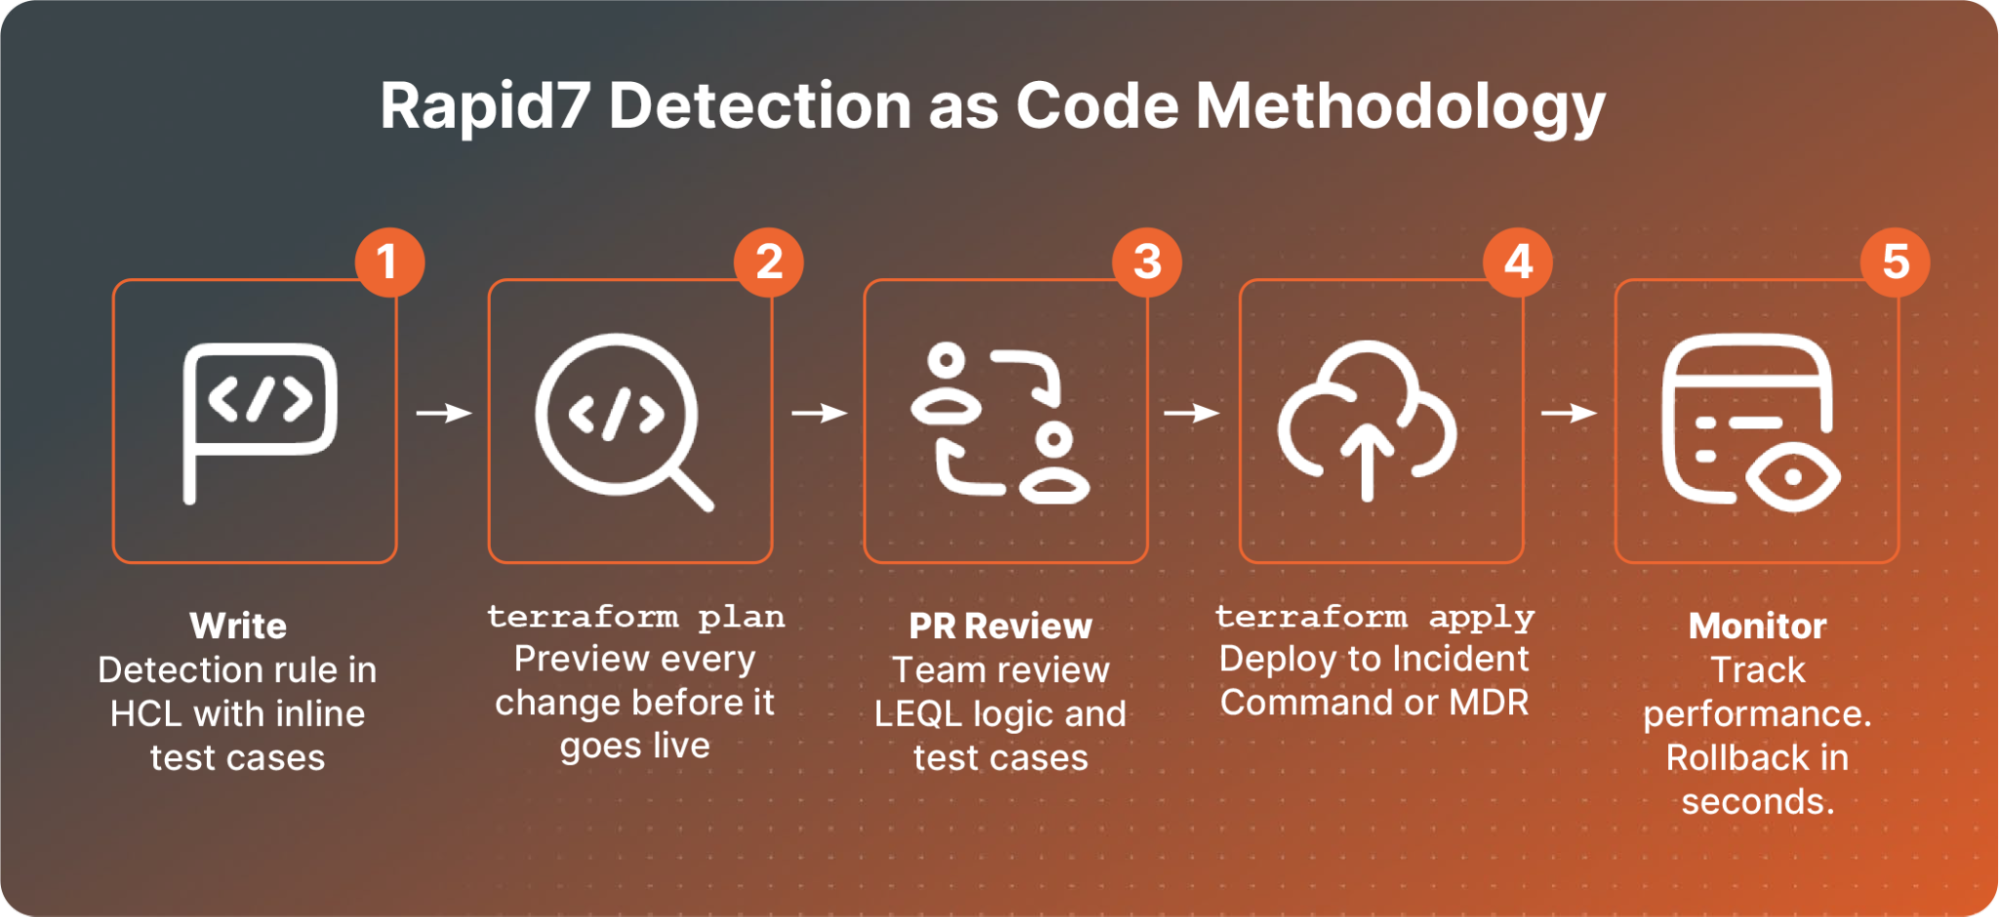
Confidently scale detection engineering with Detection as Code
Detection as Code enables security teams to build, test, version, and deploy detections using Terraform and modern engineering workflows. Built-in validation, guardrails, and version control help teams deliver higher-quality alerts, maintain more consistent coverage, and scale detection engineering more effectively.
Figure 1: Rapid7’s Detection as Code methodology.
Strengthen ransomware resilience with Ransomware Prevention for Incident Command
Ransomware Prevention for Incident Command adds an intent-based layer of protection designed to stop ransomware encryption and endpoint damage before they disrupt operations. Built into the Insight Agent, this capability strengthens ransomware resilience while working alongside existing endpoint security investments, without adding operational complexity.
Compliance
New solutions webpages
Across the globe, cybersecurity regulation is shifting away from static compliance checklists and toward ongoing risk management that blends proactive defense with effective detection and response. Rapid7’s platform, which brings exposure management and CTEM together with detection, response, and MDR, is well positioned to help organizations operationalize compliance across mandates such as NIS2, NIST CSF 2.0, DORA, HIPAA, HITRUST, and GovRAMP. To support that effort, Rapid7 has launched an updated library of dedicated compliance solution pages that map platform capabilities to the requirements that matter most across industries and regions. The first set of pages is live now, with more to follow in the coming weeks.
Figure 2: Rapid7’s new GovRAMP compliance solutions page.
Exposure management
Turn prioritized exposures into remediation progress
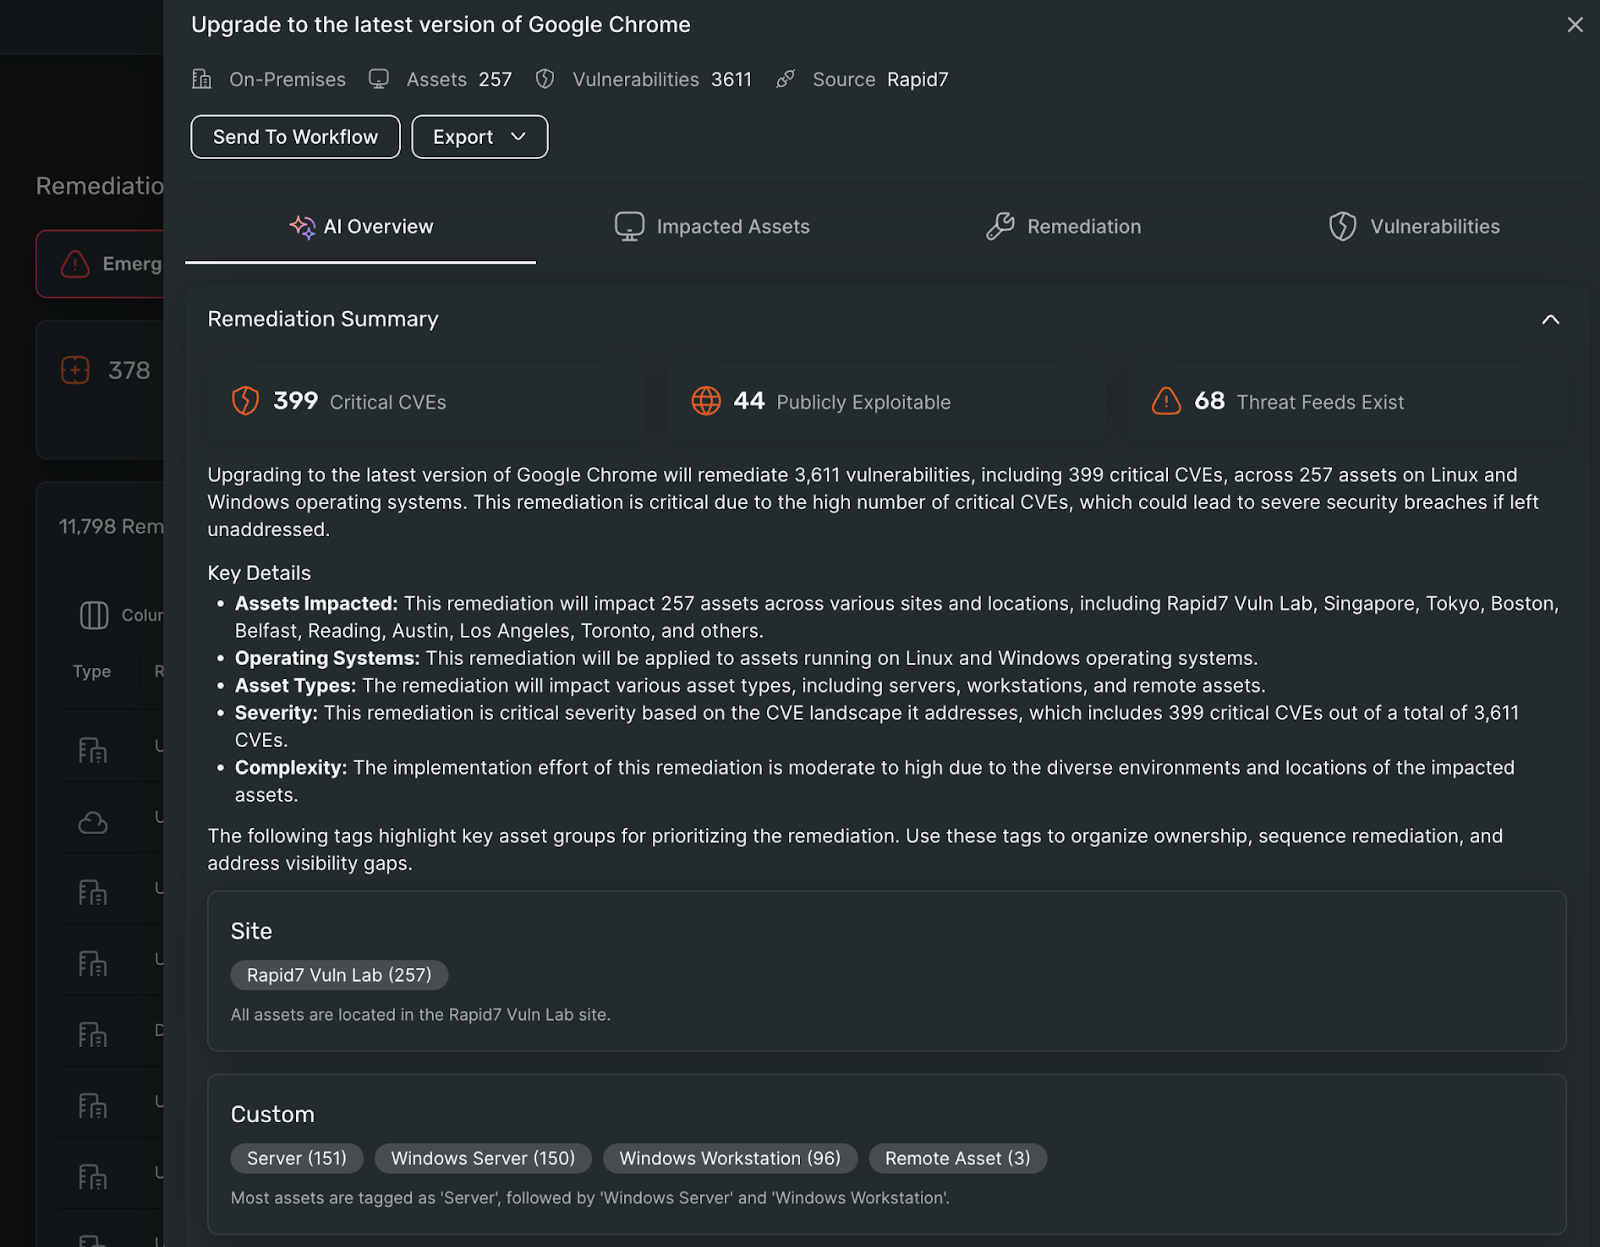
We improved Remediation Hub to help teams turn prioritized exposures into more actionable remediation progress. Updates to the Top Remediations Report add asset-level context, including operating system, IP address, cloud provider, tags, endpoint protection, and patch management details, so teams can better understand what needs to be fixed and who needs to act.
With clearer patch and endpoint coverage signals, reboot status, customizable filters, exportable reports, and scheduled email delivery, teams can spend less time assembling manual updates and more time tracking the remediation work that reduces risk. Read the full blog to learn more about how Exposure Command helps teams move from prioritized exposures to remediation progress.
AI pre-triage for AppSec findings
Rapid7 is also making application security testing faster and more focused with AI vulnerability pre-triaging for InsightAppSec. Available now for AppSec customers in supported regions, the capability uses AI to automatically remove false positives during the scan process, helping teams spend less time manually reviewing findings and more time remediating actual risk.
Initial coverage started with BlindSQL, and the latest engine release adds AI validation for BlindNoSQL findings, including content-based and timing-based detections. The result is a cleaner, more confident view of application risk, so security teams can focus on high-impact vulnerabilities and accelerate remediation with less manual effort.
Attack surface management
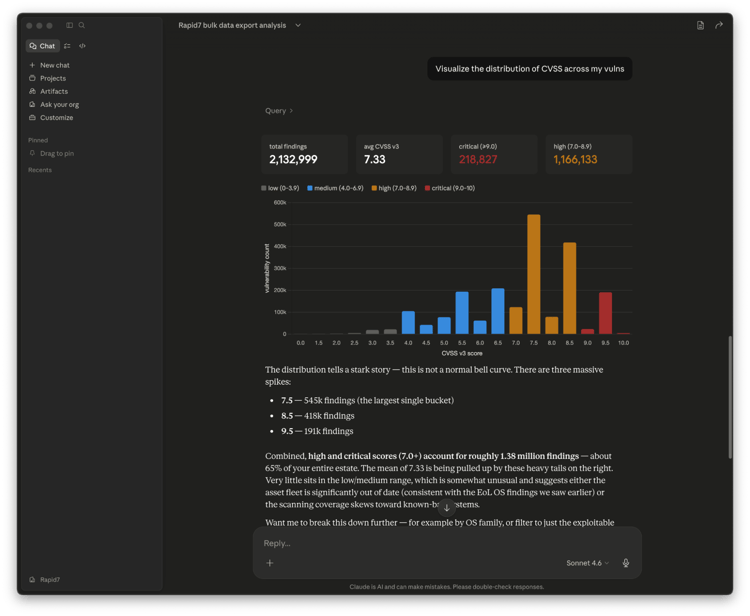
Open-source MCP Server and Agent Skill
We are delighted to announce the introduction of a free, open-source MCP Server and Agent Skill for Bulk Export. Bulk export is a highly efficient way to access all your Rapid7 vulnerability and exposure data to AI assistants and custom AI workflows. Built as an open-source bridge, it helps customers bring their Rapid7 data into the tools and experiences that work best for their teams. Check out our blog for more detail.
Figure 3: Agent Skill for Bulk Export.
Turn exposure filters into live dashboards
Surface Command also made exposure reporting easier with filter-based dashboard widgets. Teams can now turn saved asset and identity filters into live dashboards without writing Cypher queries, making it faster to track high-risk internet-facing assets, identity-driven exposure hotspots, unmanaged cloud infrastructure, and business-unit risk.
For continuous threat exposure management programs, this helps teams move from one-off reporting to repeatable, always-on views of exposure risk and remediation progress. Read this blog to learn more.
Platform and Labs
Rapid7 Command Platform
Cyber GRC
Rapid7 introduced Cyber GRC to select customers in Q2, giving teams an early look at a new way to connect security, risk, compliance, and third-party risk management in one program. Available to both Exposure Management and Detection and Response customers, Cyber GRC brings governance and compliance workflows closer to the security data teams already use every day.
Cyber GRC will be broadly available in late July. It helps organizations move toward continuous compliance by mapping controls to real environment telemetry, automating evidence collection, and prioritizing risk with live attack surface context. That means teams can spend less time chasing audit artifacts, screenshots, and vendor risk details, and more time understanding which controls, assets, third parties, and risks need attention now.
Rapid7 Labs
Rapid7 Quarterly Threat Landscape Report
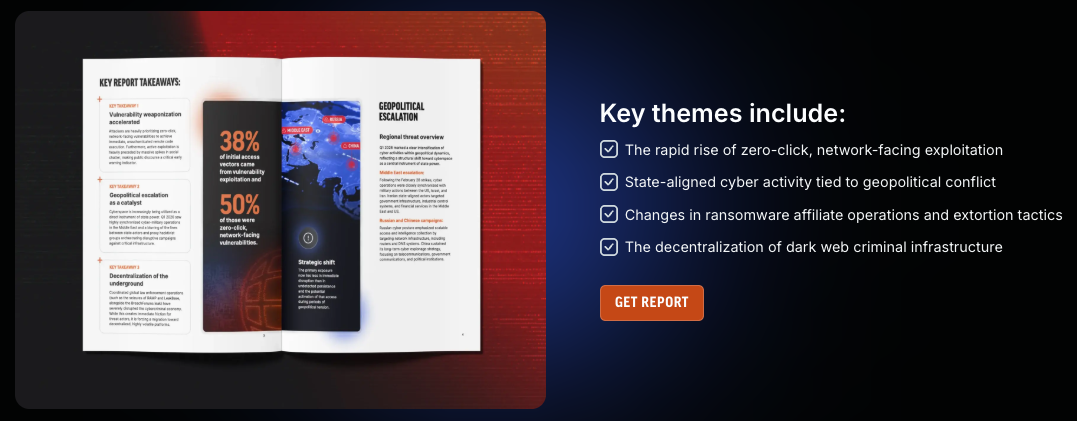
The Rapid7 Quarterly Threat Landscape Report examines the key trends shaping today’s threat landscape, drawing on MDR incident response, vulnerability intelligence, ransomware monitoring, and dark web telemetry. Q1 2026 data highlights the growing dominance of vulnerability exploitation as an initial access vector, the rise of zero-click vulnerabilities, evolving ransomware operations, and the accelerating pace at which attackers operationalize newly disclosed vulnerabilities. Read the report to explore all key findings and takeaways.
Figure 4: Rapid7’s quarterly threat report.
The latest threat research
Rapid7 researchers explored emerging trends shaping the threat landscape, including the growing commercialization of criminal AI-as-a-Service and the evolving tradecraft of advanced threat actors. From the underground adoption of AI tools for fraud and social engineering to an in-depth analysis of the Dropping Elephant malware campaign, these reports provide actionable intelligence on how attackers are adapting their techniques and what defenders can do to stay ahead.
Emergent Threat Response
This quarter’s Emergent Threat Response (ETR) coverage highlights a sustained wave of high-impact vulnerabilities affecting widely deployed enterprise technologies, including Oracle PeopleSoft, Palo Alto Networks PAN-OS, Check Point VPN, Ivanti Sentry, cPanel/WHM, and Nginx UI. For each of these CVEs, Rapid7 tracked active exploitation and rapidly evolving attacker activity to provide timely guidance to help defenders assess risk and respond quickly. See all the details, and our latest ETR coverage, here.
From strengthening detection and response to advancing exposure management, expanding governance capabilities, and delivering actionable threat intelligence, Q2 demonstrated Rapid7’s continued focus on helping security teams do more with less complexity. Every enhancement this quarter was designed to reduce manual effort, surface the context that matters, and help organizations make faster, more confident security decisions. We’re carrying that momentum into the rest of the year, so stay tuned to our blog and releases as we continue building the security operations platform that helps defenders stay ahead of what’s next.
On July 14, 2026, SonicWall published a security advisory addressing two vulnerabilities affecting SMA1000 Series remote access appliances, including the critical server-side request forgery (SSRF) vulnerability CVE-2026-15409 (CVSS 10.0) and the high-severity code injection vulnerability CVE-2026-15410. The advisory urges customers to immediately apply the latest platform hotfix releases.
Successful exploitation of CVE-2026-15409 permits an unauthenticated attacker to open a websocket-based tunnel to arbitrary localhost-only services, while CVE-2026-15410 is a local privilege escalation that permits an attacker with access to an internal service listening on port 8188 on localhost to execute arbitrary operating system commands as root via a malicious path traversal-based remove_hotfix workflow.
Both vulnerabilities are being actively exploited in the wild. Prior to SonicWall’s official vulnerability disclosure, Rapid7’s Managed Detection and Response team observed active, targeted zero-day exploitation of internet-facing SMA 1000-series appliances. In the SonicWall advisory, exploitation in the wild was noted, and both CVE-2026-15409 and CVE-2026-15410 have been added to CISA’s Known Exploited Vulnerabilities (KEV) catalog. Given the confirmed exploitation activity and the critical unauthenticated impact of the vulnerabilities, organizations should prioritize remediation of SMA1000 appliances on an emergency basis. A Python proof-of-concept for CVE-2026-15409 is available here for exposure validation, and a Metasploit module for the chain is in development.
Affected products include SonicWall SMA1000 Series models 6210, 7210, and 8200v running:
12.4.3-03245
12.4.3-03387
12.4.3-03434 (platform-hotfix)
12.5.0-02283
12.5.0-02624
12.5.0-02800 (platform-hotfix)
These vulnerabilities do not affect SSL VPN functionality on SonicWall firewalls or the SMA 100 Series product line.
Technical overview
The primary vulnerability is in a websocket proxy feature, accessed via the path /wsproxy on the affected “SonicWall WorkPlace” application (served on port 443 by default). This feature permits a netcat-like TCP tunnel to arbitrary hosts and ports, which are provided by the user in URL parameters. By providing host values that point to localhost, the attacker can access local SonicWall appliance system services behind the firewall to send and receive arbitrary TCP traffic to and from them. This is the first-stage vulnerability, CVE-2026-15409, that Rapid7 MDR analysts are seeing attackers exploiting in the wild. With this capability, an attacker can reach and exploit less-hardened services running on the appliance, such as the Erlang application on localhost:1050 or the ctrl-service application on localhost:8188.
We developed an exploit targeting the Erlang process listening on localhost:1050 for remote code execution. Note that the provided cookie value is hardcoded for the Erlang process, based on our testing, so authentication is not required to establish code execution.
With code execution established, the attacker can escalate to root on the appliance by exploiting CVE-2026-15410, which is a path traversal in the remove_hotfix workflow of ctrl-service. This can be performed via the web console or by hitting port 8188 on the device. The attacker provides a hotfix value containing a path traversal sequence to a malicious script, such as “../../../../var/tmp/privesc”. The system executes the script as root and (typically) reboots the appliance immediately after. An example malicious request achieving privilege escalation by leveraging this from the web panel is depicted below:
If the provided hotfix file does not exist, a reboot does not occur. If the provided file exists, the system reboots after it chmods and executes the file. Below is a system monitor (pspy) depicting output of this occurring during exploitation:
A Python proof-of-concept for CVE-2026-15409 is available here; a Metasploit module for the chain is in development.
Mitigation guidance
Organizations operating SonicWall SMA1000 appliances should immediately upgrade to the latest platform hotfix releases.
Fixed versions are:
Product
Fixed Version
SMA1000 Series (6210, 7210, 8200v)
12.4.3-03453 (platform-hotfix) or later
SMA1000 Series (6210, 7210, 8200v)
12.5.0-02835 (platform-hotfix) or later
There are no workarounds available.
Because active exploitation has been confirmed, organizations should not rely solely on patching. SonicWall additionally recommends:
Performing a thorough forensic review for indicators of compromise.
Re-imaging physical appliances or redeploying virtual appliances if compromise is identified.
Changing user and administrator passwords.
Resetting TOTP tokens following confirmed compromise.
Customers should consult the SonicWall security advisory for the latest remediation guidance and platform hotfix availability.
Observed exploitation
Prior to SonicWall’s official vulnerability disclosure, our Managed Detection and Response team observed active, targeted exploitation of internet-facing SMA 1000-series appliances. Threat actors were primarily leveraging the perimeter appliance as a stealthy initial access vector, executing commands on the operating system by bypassing traditional input validation controls. Once they established a foothold on the appliance, the actors systematically extracted high-value credentials, active session databases, and Time-Based One-Time Password (TOTP) multi-factor authentication (MFA) seed configurations. This local harvesting was designed to ensure long-term, persistent access that could survive standard network-level remediations.
With these harvested resources, the threat actors quickly shifted to lateral movement, pivoting from the compromised appliance directly into the internal corporate network. Specifically, we observed a sequence of anomalous, VPN-less Active Directory authentications targeting core domain controllers. These authentications originated directly from the appliance’s internal IP address, using atypical, non-corporate workstation client names (such as kali or other non-inventory hostnames) under the context of the appliance’s integrated LDAP service account. This unique behavior of direct, machine-level lateral movement with no corresponding active VPN tunnel confirmed that the appliance itself had been fully compromised and was acting as an unmonitored backdoor into the corporate directory infrastructure.
Artifacts or evidence sources and IOCs
Rapid7 recommends reviewing appliance logs for evidence of active exploitation, including the following characteristic behaviors and specific log indicators:
Characteristic Behaviors
Websocket exploit IOC log patterns: extraweb_access.log entries containing the strings (“GET” AND “wsproxy” AND “=-3389” AND “ 101 “) indicate interactions with the niche affected service. If suspicious host parameter values such as “0.0.0.0”, “localhost”, or “::ffff:127.0.0.1” are present, that’s indicative of likely exploitation of CVE-2026-15409. Note that “serviceType=SSH” was used in our published materials, but options such as “serviceType=TELNET” are viable alternatives.
Hotfix removal exploit IOC log patterns: The ctrl-service.log shows the hotfix-removal utility (/usr/local/bin/remove_hotfix) being invoked with traversal sequences pointing to attacker-staged shell script payloads (e.g., ../../../../../../tmp/sma1000_5c47.sh). This is indicative of successful exploitation of CVE-2026-15410.
Internet-facing probing: Enumeration of the SMA portal, including repeated requests to /auth1.html, path-traversal attempts, and generic file/enumeration requests (e.g., /.env, /api/sonicos/is-sslvpn-enabled).
Authentication activity: Authentication-API activity against /__api__/logon/<session-id>/authenticate.
Sensitive path access: Access to sensitive appliance paths such as /tmp/temp.db*, consistent with theft of stored session data.
AD/Service Account Compromise: NTLM logons (Windows Event ID 4624, logon type 3) into internal domain controllers sourced from the appliance’s internal IP address, using attacker-controlled workstation names (e.g., kali) without a corresponding VPN session.
extraweb_access.log: Requests to /__api__/login or /__api__/logout returning HTTP 200, and requests to /wsproxy containing suspicious host parameters returning HTTP 101.
Configuration artifacts
/var/lib/unit/conf.json containing routes for /__api__/login or /__api__/logout, which are not present in legitimate configurations.
Atomic Indicators
F.N.S Holdings Limited (ASN – 206092): The threat actor(s) utilized varying IP addresses, but they belonged to the VPN hosting provider FNS Holdings Limited. Limit or block access to FNS Holdings Limited if there is no business need. For reference, the IP addresses we observed were:
45.131.194.0/24
45.146.54.0/24
63.135.161.0/24
173.239.211.0/24
193.37.32[.]179
193.37.32[.]214
216.73.163[.]151
216.73.163[.]158
If any indicators of compromise are identified, organizations should treat the appliance as compromised and follow SonicWall’s recovery guidance.
Rapid7 customers
Organizations should prioritize identifying all internet-facing SonicWall SMA1000 appliances and determine whether affected software versions remain deployed. Given SonicWall’s and Rapid7’s confirmation of active exploitation, exposed appliances should be considered high-priority assets for remediation.
Security teams should also review available authentication, web access, and appliance management logs for the indicators published by SonicWall to determine whether follow-up incident response activities are warranted.
Exposure Command, InsightVM, and Nexpose
Exposure Command, InsightVM, and Nexpose customers will be able to assess exposure to CVE-2026-15409 and CVE-2026-15410 with authenticated vulnerability checks available in the July 15 content release.
Gopan Sivasankaran is Regional Director, Middle East & Africa, at Rapid7
From AI adoption and cloud-first strategies to smart cities and critical infrastructure modernization, organizations across the United Arab Emirates are embracing innovation at an unprecedented rate. The country truly is setting the pace for digital transformation.
Against this backdrop of rapid innovation, today’s security teams are managing increasingly complex environments while defending against more sophisticated, AI-enabled threats. In this environment, business leaders still expect security to enable innovation, not slow it down. They’re pushed to reduce risk, improve visibility across expanding attack surfaces, and respond faster than ever before, with limited resources now table stakes.
This shift is changing what organizations expect from their cybersecurity partners, with customers no longer wanting disconnected tools or transactional relationships. They’re instead craving trusted advisors who can help simplify security operations, strengthen cyber resilience, and deliver measurable outcomes.
That’s why Rapid7 is excited to announce a new strategic, Middle East-spanning distribution partnership with Mindware.
A shared commitment to the region
The Middle East continues to establish itself as one of the world’s most ambitious digital economies. As organizations invest in cloud technologies, AI, and connected infrastructure, cybersecurity has become a critical foundation for sustainable growth.
This is precisely why Rapid7 has continued to invest in the Middle East: We recognize the region’s growing importance to the global cybersecurity landscape, and this new partnership with Mindware represents another important step in that journey.
This collaboration is about more than expanding our channel presence, it’s about investing in the partners helping organizations navigate an increasingly complex security landscape.
Mindware has built a strong reputation as one of the Middle East’s leading value-added distributors, combining deep regional expertise with technical enablement, professional services, and an extensive partner ecosystem. Together, we’re creating a framework that helps partners grow their cybersecurity practices while delivering greater value to customers.
Building stronger security operations
Security teams today face a common challenge: too many tools, too many alerts, and not enough time. Organizations are increasingly looking for platforms that bring exposure management, threat detection, and response together to improve visibility and reduce operational complexity.
Rapid7’s AI-powered cybersecurity operations platform helps organizations unify security operations, reduce risk, and respond to threats with greater speed and confidence. Combined with Mindware’s regional market knowledge, partner enablement capabilities, and technical expertise, this partnership will make it easier for organizations across the Middle East to access modern cybersecurity operations through trusted local partners.
For those partners, this creates new opportunities to expand managed services, strengthen technical capabilities, and help customers modernize their security operations while supporting long-term business growth.
Local expertise alongside global innovation
The most successful cybersecurity partnerships combine global innovation with local knowledge. Organizations want world-class technology, but they also expect partners who understand their business environment, regulatory landscape, and operational priorities.
By combining Rapid7’s cybersecurity innovation with Mindware’s established regional ecosystem, we’re helping partners fortify and deliver solutions capable of addressing today’s unprecedented security challenges and threats.
Together, we’ll invest in partner enablement and technical training programs designed to help build stronger security practices and create long-term customer success.
Looking ahead
Cyber resilience is no longer just a technology objective; it’s a business imperative. As organizations across the Gulf continue to accelerate digital transformation, security teams need solutions that reduce complexity, improve operational efficiency, and help them stay ahead of an evolving threat landscape.
Rapid7 and Mindware share a common belief that the future of cybersecurity is built through collaboration. By bringing together global cybersecurity innovation, regional expertise, and a shared commitment to partner success, we’re helping organizations across the Middle East strengthen cyber resilience while enabling partners to grow with confidence.
We’re excited about what’s ahead and look forward to working with our partners to build a stronger cybersecurity ecosystem across the region.
Ready to grow with Rapid7? Learn more about the Rapid7 PACT Partner Program and discover how we’re helping partners deliver stronger cybersecurity outcomes across the Middle East.
The shift toward preemptive security is underway, but most organizations are still navigating the realities of limited resources, fragmented tools, and emerging AI risk. At Rapid7’s recent Global Security Summit, we surveyed attendees to better understand where security leaders and practitioners stand today, what is shaping their priorities, and what they need to move forward. Their responses offer a candid view into the current state of security operations: ambitious, increasingly AI-aware, and ready for change, but still working through the practical challenges of getting there.
For many teams, the direction is clear: security needs to become more proactive, more connected, and more resilient. Attackers are moving quickly, environments are expanding, and teams are under pressure to reduce risk before it turns into business disruption. But the survey results show that most organizations are still somewhere in the middle of that journey.
Where organizations are today
One of the clearest findings is that security operations are increasingly collaborative. According to the survey, 57% of respondents operate in a hybrid internal and MDR model. That reflects a reality many teams know well: internal expertise remains essential, but external support can help extend coverage, add specialist knowledge, and support faster response when internal resources are stretched.
This hybrid model also speaks to the complexity security teams are managing. Modern environments span cloud, identity, endpoints, applications, third parties, and expanding attack surfaces. Keeping watch across all of it requires more than tooling alone. It requires the right mix of people, process, visibility, and support.
At the same time, many organizations are still working to connect the dots across their security ecosystem. Two-thirds of respondents said their security capabilities are only partially integrated. For analysts, partial integration often means more manual work: switching between tools, stitching together context, and making decisions with an incomplete picture. When teams are jumping between systems, manually stitching together context, or working from incomplete data, it becomes harder to act at the speed modern threats demand.
The survey also showed that only 10% of respondents describe their organization as “highly proactive” in predicting and preventing threats, which points to the reality of where many teams are today. The ambition is there, but becoming truly preemptive takes time, integration, and operational maturity. Most organizations are still balancing the day-to-day demands of reactive response with the longer-term work of building a more proactive security model.
Confidence levels tell a similar story. 59% of respondents said they are only somewhat confident in their organization’s ability to prevent attacks before impact. Security teams understand what is at stake, but many still lack full confidence that they can consistently stop threats before they affect the business.
AI is a priority, but trust matters
AI was, of course, another major theme in the survey. Interest is high, especially when it comes to improving efficiency, accelerating triage, and helping teams manage growing volumes of data and alerts, but adoption is still developing. 52% of respondents said AI is in early-stage exploration within their security operations.
AI has clear potential in the SOC and across security operations, from summarizing investigations to enriching alerts, supporting prioritization, and helping analysts move faster. But security teams have to be deliberate about how they apply it. In high-pressure environments where accuracy, context, and accountability matter, AI needs to earn trust.
The survey results show that trust is still a key consideration. 57% of respondents cited securing AI usage as a top AI and security concern, while 44% cited lack of transparency or trust. These responses reflect a practical mindset. Security leaders are thinking about both sides of AI: how it can help defenders move faster, and how to manage the new risks it introduces. Internally, for AI to become operationally valuable, it has to fit into existing workflows, provide explainable outputs, and support human expertise.
What security teams want next
When respondents were asked what is preventing them from becoming more proactive, the top challenges were practical and familiar. 54% cited limited staff or expertise, making capacity one of the biggest barriers to progress. Teams may have the ambition to become more preemptive, but many are already balancing daily alert queues, incident response, vulnerability backlogs, compliance pressure, and business-as-usual security demands.
Visibility is another major factor. 31% of respondents cited lack of visibility across the environment as a barrier to becoming more proactive. Without a clear view of assets, identities, exposures, and attacker activity, teams struggle to prioritize what matters most. This is especially important as organizations look to move from broad detection toward more risk-aware, preemptive action.
The priorities respondents selected show where they want to go next. 41% selected preemptive security as a top security leadership priority, while improving resilience, strengthening incident response, reducing complexity, and improving risk visibility also appeared as recurring themes.
The findings from our Global Security Summit make one thing clear: security teams are ready to move toward more proactive, integrated, and AI-enabled operations, but they need the right visibility, expertise, and confidence to do it well.
To hear more from the experts and practitioners who joined us at the summit, catch up on the on-demand sessions. And to learn how Rapid7 is helping organizations move toward preemptive security, explore Rapid7 Managed Detection and Response, built to disrupt attackers earlier with broad ecosystem coverage, risk visibility, expert guidance, and an AI-powered SOC.
Not all managed detection and response (MDR) solutions are equal. Finding the differences between vendors can be quite hard, and then understanding how those differences impact your business can be even harder. For instance, you may come across an MDR provider whose pricing is based on how much data you ingest rather than the number of assets you protect.
Ingestion-based solutions have the potential to be more cost effective if you’re selective about what security telemetry you ingest – but then who analyzes the impact of the logs you’re leaving out until they’re needed?
Or, consider an MDR solution that’s more EDR with just a few additional log sources. For some organizations this is a perfectly optimal fit. But, how often are logging blind spots reviewed and accepted as a risk? In my experience, very rarely.
I like to spend time educating customers on the importance of defense in depth, and partners on how to clearly demonstrate its importance when it comes to catching and stopping attacks.
The Swiss Cheese model
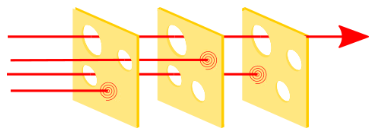
One of my favorite ways of explaining defense in depth is the “Swiss Cheese model.”
Figure 1: The Swiss Cheese model
⠀
It’s a risk model successfully used across industries like aviation safety, engineering and other domains. Its guiding principle is that a single safeguard is not fool-proof when it comes to mitigating accidents, and that true resilience is dependent upon multiple layers of monitoring and control.
The great thing about this model is that it translates really well when it comes to security operations and the technologies (SIEM) and services (MDR) that underpin it. In the case of these solutions, each slice of “cheese” is a combination of log source and detection rules across multiple attack surface domains – think endpoint, identity, cloud, or network – each reinforced by multiple log sources and detection rules that ladder up to those domains.
The log source is half of the “cheese layer,” providing the raw information.
The detection rules that help us spot attackers’ actions are the other half of the “cheese layer.”
The logs and detection rules working in combination is what represents the whole slice of cheese.
For example, let’s say you have an agent capturing activity on all of your servers and endpoints. But, an attacker has managed to steal some VPN credentials to log in to your corporate environment like a normal user. There is no agent on the attacker’s machine, only on corporate users’ machines.
Their next step is to enumerate the environment, which can be a combination of passive monitoring and active scanning. Their task? Finding that next stepping stone so they can ultimately make their way to gaining domain admin credentials or exfiltrating data from the environment as an example.
There are lots of activities the attacker can implement to achieve this without alerting any agents.. But, what if we have some log sources monitoring active directory, firewall/VPN access, and even a network-based sensor monitoring traffic going in and out of the firewall? It means we can gain additional visibility, capturing this malicious activity before it escalates.
Other methods of initial access – like phishing – can also be captured through adding log sources for email solutions and any other email-related activities. An example could be changing email inbox rules so that an unsuspecting user can’t see all the replies to the emails the attacker is sending from their mailbox.
What are the “holes” of the cheese slice?
Not every log source is able to capture every malicious activity from an attacker, which is why we need multiple layers. The holes can be for a few reasons – visibility gaps in the log source e.g. if you only have your EDR installed on 90% of the assets that can have it installed there is a clear hole. There are also detection rule shortfalls – either a rule does not exist to alert on that activity when it occurs or perhaps the log source is limited in how it records the behavior which makes creating a detection not possible.
This the whole foundational principle of Swiss cheese theory, that we should expect an attacker to be able to circumvent a single layer
How do we know what log sources and detections we need?
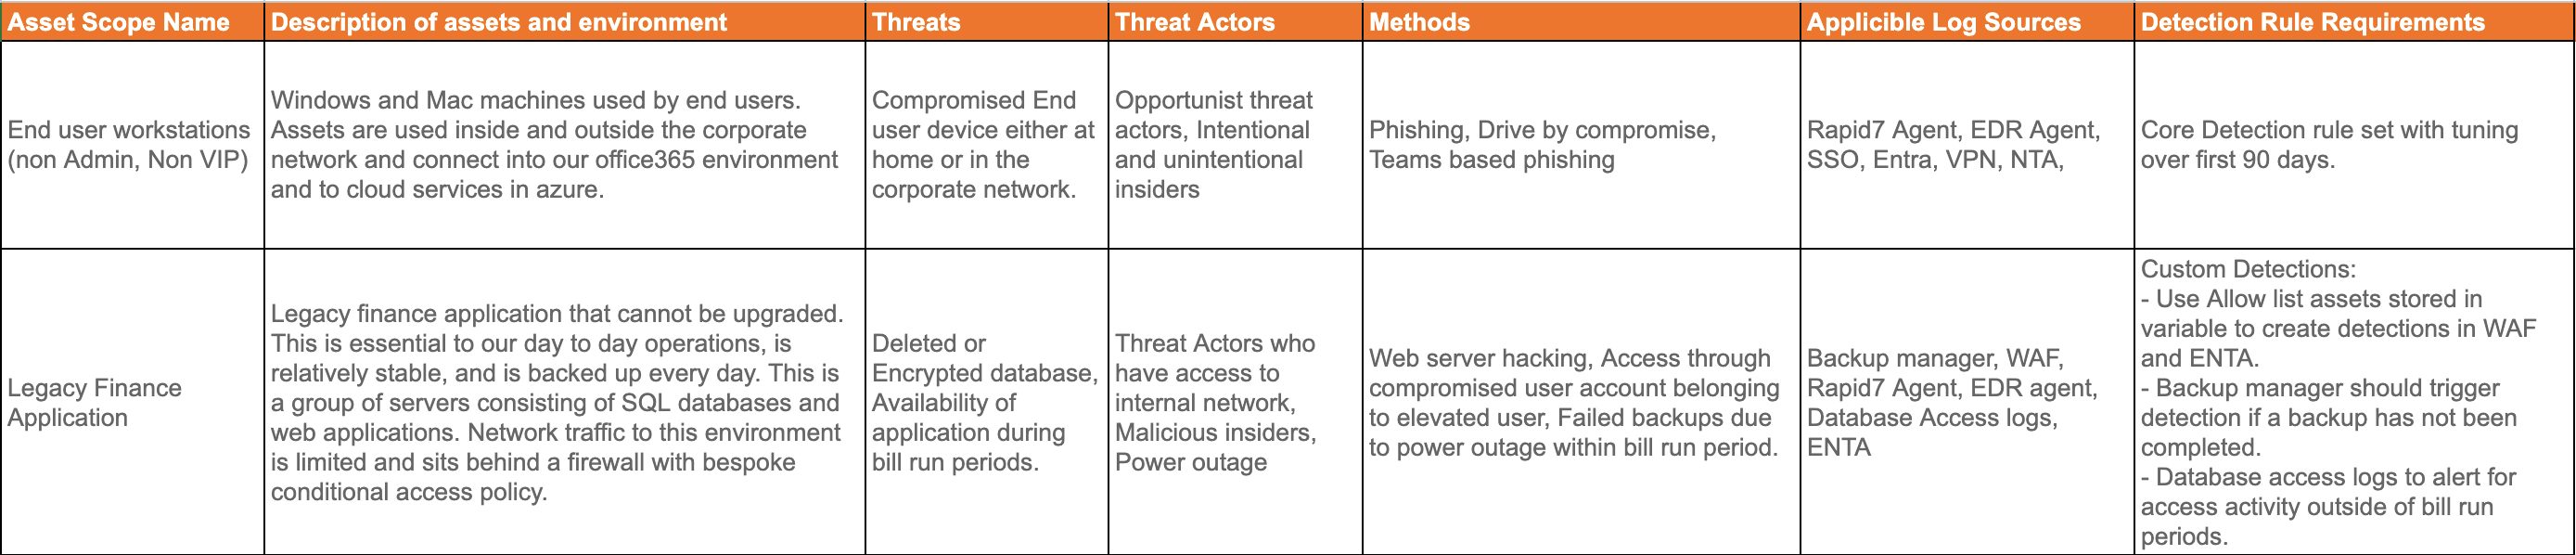
For each type of asset in your environment, it’s a great idea to draw up a Threat Model. For the purposes of this blog, the below model is fairly high level. An organization-specific threat model should go more in depth, but hopefully you can get the general idea.
Group types of assets together where it makes sense. For instance:
Windows and Mac work stations
Billing servers
CRM
Network equipment and firewalls
Domain controllers
Think about how an attacker might attempt to use these assets either to monetize the environment (i.e. ransomware) or as a stepping stone to a more critical asset.
Think about the log sources that would contribute towards highlighting attacker activity on those assets. For instance:
Windows and Mac workstations
EDR agent
Email logs
VPN/firewall authentication logs
Single sign on (SSO) logs
Domain controller
Lightweight directory access protocol (LDAP) and Active Directory logs
EDR agent
Network sensor
As I stated, this is high-level and not exhaustive, but the idea is to think of the attacker’s actions and all of the potential log sources that could detect those actions in order to ensure you’re able to capture this activity.
Of course, this model might come under scrutiny when looking at the costs of ingesting and storing log data. Organizations then have to balance the cost of technical detections with the value they provide. In real terms, if you must choose three out of five log sources because that’s what you can afford, you should pick the three most valuable to your business.
The value should come from a combination of the number of detections they drive and the quality of those detections. For example, one log source might drive 1,000 detection types, but the detections themselves have a high benign positive ratio (say 29 in 30 are benign) on 80% of the detections, whilst another log source might drive 500 detections but have a much lower benign positive ratio of 1 in 10. This forces detection engineers to create the most optimal log-and-detection rule sets in order to optimize the cost of the SIEM.
Cheese with a complex flavor is nice, overly complex MDR pricing is not
All those calculations above sound complex, right? Much of that complexity can be made simpler with an asset-based pricing model, such as the one used by Rapid7.
The price is fixed on the number of servers and workstations, and customers can connect any number of log sources. This means when you’re modeling threats and detection of those threats, there are no cost constraints to consider for onboarding additional log sources, which would improve detection fidelity.
With that in mind, here’s a few questions I would suggest customers ask themselves to establish which solution is the right one for them:
Size: How big are you in terms of employees or number of assets?
A 5,000 employee business with a 20 person Security team is more likely to need a SIEM with unlimited ingestion than a 20 person business with one combined IT/security person.
Assets and tech stack: What types of assets are being protected and what technologies are in use?
This helps dictate whether an EDR with a few extra log sources is more suitable as the backbone of an MDR service versus One that incorporates a wide variety of telemetry sources.
Whilst the lines aren’t clear cut, these can be general areas to investigate and better understand. Other factors that also come into play are things like the type of threat actors that might target your organization. Here is an example of what it could look like worked into a threat model I spoke about.
Tap to enlarge image
Comparing solutions
Attempting to compare asset-based and ingestion-based solutions can be tricky. If you try to constrain to a consistent set of log sources for the two solution types, you could be depriving your organization of the main benefit of an asset-based pricing structure: the ability to bring more log sources and detections – and therefore additional layers of protection – for the same cost. This would, of course, give you a lower cost-per-detection. Let’s take a look at some ideas that might help:
Look at cost-per-detection when fixing a cost limit.
For example, you take the asset-based structure and solution cost, and configure an equivalent cost on an ingestion-based solution. You then look at how many log sources and detections that gets you, then calculate the cost-per-active-detection. It’s also best to model this on your own or potential customers’ environments.
Evaluate quality of detections within the model environment using the cost model constraint.
Running the same offensive exercises in the same environment is a fair test to run, so in this instance you should set up all the log sources for each model up to your cost constraint. Keep in mind you will likely have more log sources for an asset-based model. This is still a fair test, as our key comparison metric is total cost of the solution regardless of how that solution detects the attacker.
Detection noise under normal conditions.
This is an indication of the quality of the detection rules under normal conditions. It’s great to detect attackers in an isolated environment, but in a production network with users working, it may also introduce many benign or false positives that the same detection rules will alert on. You want your detection rules to only alert on real attacker activity.
Metric 3 – Quality 2 – rules triggered by normal user activity
Total investigations triggered in 30 days
100
130
Total True Positive investigations in 30 days
90
87
True Positive Ratio %
90%
67%
Points
40
40
0
Metric 4 – Monthly SOC operations overhead – tuning and detection rule writing (N/A for Managed)
Hourly rate
$200
$200
Tuning time in hours over the last 30 days
10
12
Detection rule writing time in hours over the last 30 days
6
8
Monthly soc operations overhead in $
$3,200.00
$4,000.00
Points
10
10
0
Metric 5 – Implementation time
Hourly rate
$200
$200
Time to implement solution in hours for example customer
40
40
Total PS cost for solution implementation
$8,000.00
$8,000.00
Points
10
0
0
Total Points
110
30
⠀
Whilst there are no absolutes, there are some good rules that can help you on the path to choosing an MDR provider that works best with and for your organization. Focusing on the assets and technologies that you want to protect, and looking at log sources and detections that support that is a great place to start.
The higher the importance and complexity of the asset, the more layers you ideally want, and having the table above to clearly define your quality metrics will help you consider whether a solution is the right fit for you in terms of technology, service, and economics.
What actually happens inside a SOC when an incident unfolds? Most teams see the alerts and the outcomes, but the decision-making in between is often less visible.
At the Rapid7 2026 Global Cybersecurity Summit, the signature session Inside the Modern SOC: Who Carries You Through an Incident takes a different approach. Rather than focusing on tools or dashboards, it follows a real-world incident from the perspective of the people responsible for investigating and containing it.
The session walks through how modern MDR teams operate under pressure, drawing on real experience across cloud, identity, and on-prem environments. Led by Karl Lankford, Senior Director, Sales Engineering, Rapid7, the discussion brings in perspectives from across the SOC, including incident response and detection, to show how teams work together when it matters most.
Structured around a full incident lifecycle, the walkthrough begins with the initial signal and moves through triage and investigation, following the decisions that shape the outcome. The focus is not on theory but on how incidents are handled in practice, from background and context through to the final result.
What stands out is how much of the process depends on judgment. Alerts are only the starting point. From there, analysts are working to understand context, assess risk, and decide what matters most in the moment. This includes identifying compromised identities, understanding how attackers move across environments, and coordinating response across multiple systems.
The session also highlights how quickly these decisions need to be made. As shown in the high-level timeline, attackers can move from initial access to broader compromise across cloud and on-prem systems in a matter of minutes, which leaves little room for hesitation or uncertainty.
Throughout the walkthrough, the focus stays on what carries organizations through an incident. Detection plays a role, but outcomes are shaped by coordination, tradeoffs, and the ability to act with clarity under pressure. The session also explores how visibility across environments, combined with human-led response, helps teams connect signals and act before impact occurs.
For practitioners, SOC leaders, and teams evaluating MDR, this session offers a grounded view of how modern incident response works under real conditions. It shows what happens between the alert and the outcome, and why that gap is where the real value lies. Watch the full session to follow the investigation step by step and see how MDR teams carry organizations through real incidents.
On May 13, 2026, Palo Alto Networks published a security advisory for CVE-2026-0257, a medium severity authentication bypass affecting PAN-OS and Prisma Access when a specific configuration is present. Successful exploitation of this vulnerability allows a remote unauthenticated attacker to successfully establish a VPN connection through the GlobalProtect gateway of an affected appliance.
Rapid7 MDR identified successful exploitation across numerous customers, however we did not observe any indication of successful lateral movement from the devices. The earliest date for observed exploitation was May 17, 2026.
While the assigned CVSSv4 score indicates a medium severity, due to the circumstances surrounding this vulnerability Rapid7 urges that organizations treat this as a critical vulnerability. An authentication bypass in an edge facing enterprise VPN appliance can have significant impact to affected organizations. As such, organizations running affected appliances are urged to upgrade to a vendor supplied patch on an urgent basis.
Observed Attacker Behavior
On 2026-05-18 01:51:37 UTC, Rapid7 MDR responded to a ‘Suspicious VPN Authentication – Local Account Logon via Generic Non-Human Identity’ alert. During the initial investigation, Rapid7 observed a suspicious cookie authentication to the local admin account across multiple customer environments from the same hosting provider, Vultr.
Rapid7 MDR analyzed the Palo Alto tech support files across the impacted customers and observed that Cloud Authentication Service (CAS) was disabled and the GlobalProtect portal or gateway had authentication override cookies enabled. Based on these findings, MDR analysts concluded that this was likely exploitation of CVE-2026-0257. Subsequent analysis by Rapid7 Labs confirmed this was accurate by validating a successful proof-of-concept.
Rapid7 MDR observed a second wave of exploitation on May 21st. Due to the consistent MAC address, Rapid7 believes both waves of exploitation are likely from the same threat actor (TA). However, the second wave of compromises originated from the hosting provider, Dromatics Systems. In this wave of exploitation, Rapid7 observed VPN IP assignment following the cookie authentication, granting them access to the internal network. At this time, Rapid7 is unable to confirm why VPN assignment occurred only for a subset of exploited customers. Across multiple customers, Rapid7 observed successful exploitation to obtain the cookie, but did not observe the cookie being used to obtain a VPN session in 8 out of 10 impacted MDR customers. Rapid7 did not observe any follow-on activity in the two customer environments where a VPN session was established.
<14>May 21 01:54:39 FW-PA-A 1,2026/05/21 01:54:38,010101010101,GLOBALPROTECT,0,2818,2026/05/21 01:54:38,vsys1,gateway-auth,login,Cookie,,admin,US,DESKTOP-GP01,146.19.216.125,0.0.0.0,0.0.0.0,0.0.0.0,aa:bb:cc:dd:ee:ff,,6.0.0,Windows,"Microsoft Windows 10 Pro , 64-bit",1,,,"Auth latency: 1019ms, profile: SAML-o365-GP",success,,0,,0,GlobalProtect_External_Gateway,0101010101010101010 ,0x8000000000000000,2026-05-21T01:54:39.142-05:00,,,,,,30,241,35,0,,FW-PA-A,1,,",
GlobalProtect Authentication Log
Technical Analysis
Per the vendor advisory, we know the issue lies in a feature called “authentication override”. This feature allows a GlobalProtect portal or gateway to issue cookies to an authenticated user. The authenticated user can then use an authentication override cookie in future communications to the GlobalProtect portal or gateway in lieu of re-authenticating via credentials, akin to a bearer token. This is not a feature that is enabled by default.
We also know from reading the vendor advisory that the vulnerability requires a certain configuration in how certificates are used to encrypt and decrypt these authentication override cookies. Specifically, the certificate used to encrypt and decrypt authentication override cookies must not be the same certificate used for the GlobalProtect portal or gateway’s HTTPS service. This is a significant clue to how the vulnerability works.
To explore what an authentication override cookie looks like and how they are created, we can look at the implementation in the /usr/local/bin/gpsvc binary which implements the GlobalProtect service (Our testing appliance was running PAN-OS 10.2.8 in a vulnerable configuration). Inspecting the main_DoAuthLogin function, we see that if a HTTP form value of either portal-userauthcookie or portal-prelogonuserauthcookie is present during a POST request to /ssl-vpn/login.esp, authentication will be performed by a call to main_AuthWithCookie. This function will take the incoming encrypted cookie value stored in either portal-userauthcookie or portal-prelogonuserauthcookie, decrypt it and extract the cookies user name, domain name, host id, client OS, remote address, and timestamp (as auth override cookies have a lifetime after which they will expire).
If we look at the main_DecryptAppAuthCookie function we can begin to see the problem. The incoming encrypted cookie is base64 decoded and then decrypted using a private key. The decrypted content is then trusted implicitly, with no signature verification of any kind occurring after decryption.
The implication here is that anyone who knows the public key for the certificate used by the authentication override feature to encrypt and decrypt cookies, can successfully forge and encrypt an arbitrary authentication override cookie. The question then becomes, how does an attacker learn the correct public key to use in this attack?
This brings us back to the vendor’s advisory where they state “do not reuse the portal or gateway certificate, and do not share this certificate with other features or users”.
If a GlobalProtect portal or gateway has reused the certificate for encrypting and decrypting cookies with another feature, such as the HTTPS service of the portal or gateway, then a remote unauthenticated attacker can discover the public key for that certificate. In doing so the attacker will be able to successfully forge and encrypt arbitrary authentication override cookies. As these forged cookies will be successfully decrypted server side, they will be trusted and an authentication bypass will be achieved. An attacker can use a valid forged authentication override cookie to login and establish a VPN connection.
In addition to Exposure Command and InsightVM customers being able to assess their exposure with authenticated checks, a publicly available proof-of-concept script to test if an appliance is vulnerable to CVE-2026-0257 has been developed by Rapid7 Labs. The script will retrieve all certificates in the chain for the HTTPS service of either a GlobalProtect portal or gateway. Each certificate in the chain is iterated over and an authentication override cookie is forged using each certificate’s public key. This forged cookie is then tested against the GlobalProtect portal or gateway, and the script reports back if authentication was successful or not.
The usage of the script is shown below.
$ python3 forge_cookie.py --help
usage: forge_cookie.py [-h] --target TARGET [--port PORT] [--user USER] [--domain DOMAIN] [--host-id HOST_ID] [--client-os CLIENT_OS] [--client-ip CLIENT_IP] [--context {gateway,portal,both}] [--verbose]

Forge a GlobalProtect auth override cookie using the public key from TLS (CVE-2026-0257).

options:
  -h, --help            show this help message and exit
  --target TARGET       Target GP portal/gateway IP/hostname
  --port PORT           Target port (default: 443)
  --user USER           Username to forge cookie for (default: admin)
  --domain DOMAIN       Domain for cookie (default: empty)
  --host-id HOST_ID     Host ID for cookie (default: empty)
  --client-os CLIENT_OS
                        Client OS for cookie (default: Windows)
  --client-ip CLIENT_IP
                        Client IP in cookie (default: 0.0.0.0)
  --context {gateway,portal,both}
                        Context to test: gateway, portal, or both (default target)
  --verbose             Print full response
A successful invocation of the script against a vulnerable appliance is shown below. We can see the target’s GlobalProtect gateway accepted a forged authentication override cookie using the second certificate in the chain.
$ python3 forge_cookie.py --target 192.168.86.99 --user haxor
[*] Retrieving certificate chain from 192.168.86.99:443 ...
  Found 2 certificate(s) in chain:
  [0] CN=192.168.86.99 (RSA 2048 bits, CA=False)
  [1] CN=GP-Lab-CA (RSA 2048 bits, CA=True)

[*] Forging cookie for user 'haxor', testing each key

  Trying [0] CN=192.168.86.99
  [-] Failure - Gateway did not accepted the forged cookie
  [-] Failure - Portal did not accepted the forged cookie

  Trying [1] CN=GP-Lab-CA
  [+] Success - Gateway accepted the forged cookie
  Cookie: ng9ygxlaclylNXeSHcakXZPK06Fno0svVirz6RhRtA5mDmOaZyg/KMxUuM5lRvm1Rn1Z6vqaWQQPvQOHzwJnyldOmhUKy+HDMgIYtJ/kk3ypMqmFE7BbmPxnSKxKcQQbNIcxgkrhCwuJKwybuq0aaPVNzN9BSWmh1QmZj7oLjTEo9ExAXrm951mqYhh3+MgBCScaYqP23WzrC+vzqJB74sHoMUuFWIF8/sMYDMpvENOoI4nXAFCaRYSruW9FQQy5VTzNifNWkrYcdzDCXKiP8v4G098/2QoBbVoyHBZwbgHGBsRU3ZeSgoHjrhjxyotIshKVssUs8CRpuG2HlZBM0Q==
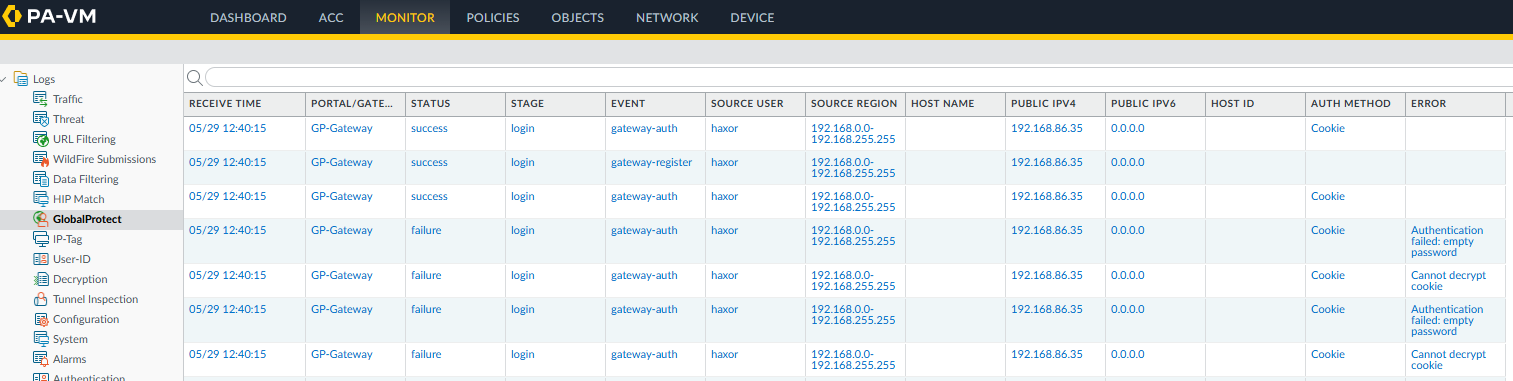
We can observe the successful authentication via the management interface, as shown below. The two initial failures correspond to the first certificate being used which was the incorrect certificate.
Figure 1: PAN-OS Management Interface
Mitigation Guidance
According to the Palo Alto Networks advisory, the following product versions are affected by CVE-2026-0257:
Product
Affected
Unaffected
PAN-OS 12.1
< 12.1.4-h6
< 12.1.7
>= 12.1.4-h6
>= 12.1.7
PAN-OS 11.2
< 11.2.4-h17
< 11.2.7-h14
< 11.2.10-h7
< 11.2.12
>= 11.2.4-h17
>= 11.2.7-h14
>= 11.2.10-h7
>= 11.2.12
PAN-OS 11.1
< 11.1.4-h33
< 11.1.6-h32
< 11.1.7-h6
< 11.1.10-h25
< 11.1.13-h5
< 11.1.15
>= 11.1.4-h33
>= 11.1.6-h32
>= 11.1.7-h6
>= 11.1.10-h25
>= 11.1.13-h5
>= 11.1.15
PAN-OS 10.2
< 10.2.7-h34
< 10.2.10-h36
< 10.2.13-h21
< 10.2.16-h7
< 10.2.18-h6
>= 10.2.7-h34
>= 10.2.10-h36
>= 10.2.13-h21
>= 10.2.16-h7
>= 10.2.18-h6
Prisma Access 11.2.0
< 11.2.7-h13
>= 11.2.7-h13
Prisma Access 10.2.0
< 10.2.10-h36
>= 10.2.10-h36
Affected products must have the authentication override feature enabled in either the GlobalProtect portal or gateway, and must reuse the authentication override cookie encryption and decryption certificate with another feature in order to be vulnerable. As a mitigation, affected products should either disable the authentication override feature or generate a new certificate to use exclusively for the authentication override feature.
Please refer to the vendor advisory for the latest guidance.
Rapid7 Customers
Managed Detection Response (MDR)
The following detection rules are available for InsightIDR and Managed Detection Response (MDR) customers:
Suspicious Authentication – Palo Alto GlobalProtect Cookie Authentication to Local Admin Account
Threat Intel (Rapid7 MDR SOC/IR) – VPN Authentication via Spoofed MAC Address
Threat Intel (Rapid7 MDR SOC/IR) – Indicator of Compromise Observed
Suspicious VPN Authentication – Local Account Logon via Generic Non-Human Identity
Suspicious VPN Authentication – Local Account
Suspicious Authentication – Vultr
Suspicious Authentication – Dromatics Systems
Exposure Command, InsightVM, and Nexpose
Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-0257 using an authenticated check available since the May 15 content release.
Known Indicators of Compromise
Low-cost hosting providers; frequent origin of sustained threat campaigns.
Item
Description
104.207.144.154
Threat actor source IP
146.19.216.119
Threat actor source IP
146.19.216.120
Threat actor source IP
146.19.216.125
Threat actor source IP
DESKTOP-GP01
Machinename observed in the GlobalProtect logs alongside Windows authentications first observed on May 21, 2026
GP-CLIENT
Machinename observed in the GlobalProtect logs alongside Linux authentications first observed on May 17, 2026
aa:bb:cc:dd:ee:ff
Spoofed MAC address observed in both waves of successful exploitation
Security leaders are operating in an environment that is only getting more complex. Expanding attack surfaces, rapid AI adoption, growing toolsets, and increasing pressure to respond faster have made it harder to maintain a clear view of risk and priorities.
At the Rapid7 Global Cybersecurity Summit, the customer panel How Clarity Beats Complexity explores how leaders are navigating that reality in practice. Drawing on perspectives from CISOs and technology leaders across industries, the session focuses on how teams are managing complexity without losing sight of what matters.
Rather than focusing on theory, the discussion is structured around a set of practical questions that reflect what teams are dealing with today. These include where complexity is making security harder to manage, how alerts, data, and handoffs are slowing decisions, and what can look like progress but fails to deliver meaningful outcomes.
As the conversation develops, speakers such as Debby Briggs, VP-CISO at Netscout Systems and Raheem Daya CTO at Target RWE share how their teams are rethinking processes, habits, and assumptions that add noise without improving security. The emphasis shifts toward questioning metrics that measure activity rather than risk, and focusing instead on what drives meaningful outcomes.
From there, the session looks at what is actually making a difference. Topics include how leaders are clarifying priorities, aligning security actions with real business impact, and where visibility and context are proving more valuable than volume. Will Lambert, Information Security Manager at Culligan International adds a practitioner perspective, highlighting how clearer ownership and better coordination across teams help reduce friction in day-to-day operations.
Throughout the session, the focus remains on practical decision-making. This includes managing complexity without oversimplifying, validating investments in areas such as MDR and consolidation, and ensuring security teams are focused on outcomes that improve resilience.
For CISOs, security operations leaders, and teams evaluating their current approach, this panel offers a grounded view of how others are tackling the same challenges.
Watch the full customer panel to hear how security leaders are cutting through complexity and focusing on what actually improves outcomes.
Managed Detection and Response (MDR) is a cybersecurity service that combines human expertise and technology to detect, investigate, and respond to threats 24/7.
I write this as a Field CISO at Rapid7, but also as someone who has had to live with the operational reality of MDR on the customer side. I have seen what happens when a service is a black box, when technology and service drift apart, and when cost, retention, and accountability are misaligned. That experience shapes the view in this piece: MDR selection is not just about buying monitoring in isolation, but about choosing a partner that can help your team reduce risk and improve the way security operates over time.
When organisations evaluate MDR, they often start in the wrong place. The discussion begins with integration counts, dashboards, pricing tables, and increasingly bold claims about AI or dramatic reductions in alert volume. Those things all matter to a degree, but they are not the centre of the decision. The real question is whether you are choosing a provider that will work as a genuine partner, help you reduce risk over time, and strengthen the way your team operates when the environment becomes noisy, complex, or difficult to manage.
That matters because MDR is not a service that sits neatly off to one side of the security function. It becomes part of the operating model. It influences how visibility is created, how incidents are handled, how priorities are surfaced, and how much confidence a leadership team has in the people and processes around it. For that reason, I do not think MDR selection is primarily a tooling exercise. It is a partnership decision.
What poor MDR looks like in practice
My own view on this has been shaped by more than one experience. In one case, our MSSP was part of a defence company that was later carved out into a separate business. The service was built around a legacy SIEM. They had plenty of interest elsewhere in automation and future-state capability, but the fundamentals were being missed. We could talk about what we wanted to automate, but not with enough confidence about the quality of the underlying visibility, the operational process around it, or how the service was supposed to mature over time.
In another case, the issue was an MSSP overlay wrapped around a well-known, high-cost log indexer. On paper, that should have been a strong foundation. In practice, the management layer around it was poor. There was a lack of expertise, no credible roadmap, and very little meaningful tuning. As the MSSP was also reselling the ingest, there was no obvious incentive to optimize data use in the customer’s favour. Ingest was capped because of cost, retention was limited to 90 days, and we were left with the uncomfortable combination of high spend, constrained visibility, and a service that did not appear to be improving in any meaningful way.
Those experiences shaped how I think about MDR because they exposed the same underlying problem. The technology was not absent, but the service model around it was weak. When the gap between the platform and the service becomes too wide, the customer ends up paying for capability in theory while carrying the operational risk in practice.
Why the gap between platform and service matters
This is where many MDR relationships start to fail. Even when the tooling is capable, the provider still has to connect platform, people, process, and commercial model into one coherent service. If that does not happen, the customer ends up living with support issues, awkward hand-offs, misaligned contracts, unclear accountability, and a constant sense that there are too many moving parts and not enough ownership.
That is why I would start any MDR evaluation by looking at how the relationship is meant to work in practice.
Does the provider genuinely own the experience end to end, or are they effectively brokering one element through another?
Can they show how the programme will improve over the first year, not just how onboarding works in the first month?
Do they understand the rest of your security ecosystem and how to operate within it, or do they assume every answer involves expanding their footprint?
Strong providers think holistically. They understand that the customer already has an environment to manage, existing tools to work with, and internal teams who need clarity rather than additional friction. They think in terms of operating model, monitoring, response, and continuous improvement over time, rather than treating the service as a thin wrapper around a platform. That is usually where the difference between coverage and real partnership becomes obvious.
Proactive defense starts with the fundamentals
True partnership is defined by its ability to deliver proactive defense and continuous improvement. By this, I do not just mean threat hunting or faster triage. I mean exposure reduction in the broader sense. It is understanding attack paths, using intelligence well, tuning detections properly, improving visibility where it matters, and building a service rhythm that reduces the conditions attackers rely on.
That sounds obvious, but it is surprisingly easy for organisations to be distracted from those fundamentals. Low entry prices often mask a fundamentally constrained operating model, shifting risk and cost back to the customer.
Sweeping promises about single digit alert volumes should be treated carefully, especially before a provider has properly understood the environment. The same is true of broad agentic AI claims. Automation can absolutely help, but it does not replace accountability, operational judgement, or the need for a provider to show how the service will improve over time.
For me, that last point is one of the clearest tests of whether the relationship is working. An MDR service should not be something you set and forget. A mature partnership should look better in month twelve than it did in month one. Visibility should improve. Tuning should improve. The roadmap should improve. Confidence in escalation and response should improve. If none of that is happening, it becomes very difficult to describe the relationship as a real partnership. At that point, you may simply have outsourced a queue.
When displacement becomes the right answer
That is also how I think about displacement. An incumbent should not be displaced simply because another provider has a sharper demo or a more fashionable story. Displacement makes sense when the existing model has stopped improving, when the service feels static or opaque, when the team lacks the expertise to tune and evolve it properly, or when the commercial structure and delivery model are working against the customer rather than with them.
If the relationship is held together by workarounds, if there is no meaningful roadmap, or if the customer is left carrying too much of the integration and governance burden themselves, the problem is usually structural rather than temporary. In that situation, the question is no longer whether the service can be tweaked around the edges. The question is whether the model is fit for purpose at all.
Consolidation is only useful if it improves the model
That does not automatically mean consolidation is the answer. Consolidation can be valuable, but only when it improves the operating model rather than simply reducing the number of logos in the environment. In some cases, the right answer will be to build a broader relationship with a provider that has earned trust and shown it can deliver more. In others, the right answer will be better integration and a clearer division of responsibilities.
What matters is whether the provider helps create a more coherent, scalable, and accountable way of operating. If consolidation leads to better hand-offs, stronger accountability, and a simpler way of reducing risk, it can be very valuable. If it does not, then consolidation is not the point. A better operating model is.
This broader view is also consistent with established security guidance. NIST CSF 2.0 frames cybersecurity as a risk management discipline across governance, protection, detection, response, and recovery [1]. NIST’s latest incident response guidance reinforces that response should be integrated into wider risk management and improved over time [2]. The NCSC makes a similar point in its guidance on building a SOC and on security monitoring, where tools, skills, and operating model all need to work together [3]. CISA’s exposure reduction guidance points in the same direction by focusing on reducing the conditions attackers rely on before incidents escalate [4].
Questions worth asking any MDR provider
There are a few practical questions I would encourage any CISO, Security Director, or Security Operations Manager to ask, whether they are reviewing an incumbent or evaluating a new provider:
How will the service improve over the first year and beyond?
Where do the hand-offs happen between your platform, your analysts, and my team?
How do you work with the security and IT tools we already rely on?
How predictable is the commercial model as coverage expands?
What are you doing to reduce risk before the next incident, not just respond after it?
If your commercial model benefits from more ingest, what incentive do you have to tune it down?
Those questions reveal far more than a polished demo ever will.
Ultimately, the organisations that get the most value from MDR tend to be the ones that treat it as part of a wider security partnership rather than a neatly outsourced function. They expect transparency, progress, and a provider that understands both the environment they have today and the operating model they are trying to build over time. That is the standard worth holding. If the provider is not improving the programme over time, you do not have a real partnership. And if consolidation does not lead to a better operating model, it is probably not worth doing in the first place.
Alan Simpson is Field CISO for the UK and Ireland at Rapid7, advising CISOs and senior leaders on cyber risk, resilience, and security strategy that supports business outcomes. Before joining Rapid7, he served as Global Security Operations Manager and Acting CISO at Keyloop, where he led security operations and wider information security initiatives. He has also held senior security leadership roles at Allianz and LV=, with experience across security operations, incident response, architecture, awareness, supplier assurance, and security testing.
In the latest episode of Rapid7’s Experts on Experts, I’m joined by Rapid7 CEO Corey Thomas for a candid conversation about where AI is genuinely changing security operations, and where the hype still outruns reality. The short version is that AI is already improving productivity in software development, but the bigger shift for security leaders is what it can do with telemetry at scale. As Corey puts it, no team of humans can process all security telemetry, all the time, across an entire environment. That gap is where AI can help, but only if the inputs are right.
We also dig into what this means for Managed Detection and Response (MDR), and why the market is moving from “watch a subset of signals” toward monitoring the full environment, 24 x 7. The catch is that raw volume is not the goal. The goal is a comprehensive data set that enables decision making under pressure, with enough context to act early.
AI is only as good as the context behind it
One theme that kept coming up in our conversation is trust. Corey explains why earlier automation and SOAR efforts struggled. They followed strict rules, but security rarely behaves in strict patterns. When something looked similar but required a different response, teams hesitated to rely on automation. The dynamic rule making that newer AI models provide can help, but only if fueled with the right context.
Corey breaks “context” into practical components: understanding what technologies are deployed, how they are configured, what controls exist, what vulnerabilities are present, and what activity is actually happening across those systems. Without that full picture, teams spend time chasing the wrong risks. He compares it to buying earthquake insurance without knowing where you live. If you are in California, it might make sense. If you are in Florida, hurricane coverage is the real concern. Context tells you which risk actually matters.
Preemptive MDR is the shift CISOs should plan for now
Where the conversation gets especially relevant for 2026 is the move from reactive to preemptive security. To frame the change in plain terms: reactive posture waits for alerts, while leaders want partners who anticipate and identify risks earlier.
Corey describes preemptive MDR as an attack surface discipline. It starts with understanding the full attack surface, spotting where attacks are likely to occur, and identifying the most attractive exposures in the environment. The operational step is what matters: identifying those exposures quickly, prioritizing realistically, and having preset remediation and response plans ready before the moment hits. Corey is direct about constraints, too. No organization can remediate everything all the time, but better planning and efficiency are still possible, and business expectations of security leaders are rising. He also notes that government and regulators are pushing in the same direction, and that Gartner and other analysts are reinforcing the shift toward anticipation rather than after the fact response.
Cloud scale forces MDR to evolve, especially around identity
We also spent time on the cloud, because it continues to reshape how security programs operate. Most organizations are building more, faster, across more cloud technologies and identities, and AI only accelerates that pace. Corey’s view is that MDR has to mirror that technology reality. At a baseline, teams need to monitor what their cloud providers already offer. He calls out identity as the harder requirement: understanding identity traffic across the environment, separating legitimate from malicious behavior, and tracking roles and responsibilities so investigations do not happen in a vacuum. If an MDR program is not looking across the cloud landscape, it cannot confidently say it is monitoring the right things, especially in the areas where new bugs and misconfigurations show up first.
Transparency becomes a differentiator when AI enters the loop
As AI becomes more present in triage and investigation, Corey argues that transparency will matter even more. He shares that Rapid7 built MDR with the assumption that customers should be able to log in at any time and audit what is happening in their environment. That level of visibility can be uncomfortable, but it becomes more important as AI plays a larger role in how decisions are made. The presence of AI in MDR programs does not reduce the need for trust, but increases it. And that trust is built through transparency and auditability, not assumption.
That also means being able to show where AI is actually making a difference. It is not enough to say it is working. Teams need to see the impact in real terms.
Corey contrasts that with what he sees as the market default: black box approaches that ask customers to trust the output until something goes wrong. His prediction is blunt and practical. As buyers mature, RFPs will demand the ability to inspect how alerts are processed and how investigations are run, because that is what trust looks like at scale.
Watch the full episode below to hear Corey’s take on what is changing, what is still missing, and why the strongest MDR programs in 2026 will be the ones that plan for preemptive action, not just faster reaction.
The Rapid7 MDR team is currently monitoring an increase in phishing campaigns where threat actors (TAs) impersonate internal IT departments via Microsoft Teams. The primary objective is to persuade users to launch Quick Assist, granting the TA remote access to deploy malware, exfiltrate data, or facilitate lateral movement across the network.
Social engineering via IT Support impersonation is not a new threat, but the recent surge in Teams-based delivery highlights a critical vulnerability in how organizations manage external access. Teams often allows any external user to message internal staff. This is the functional equivalent of operating an email server without a gateway filter. While a cautious user might notice an “External” tag on the chat, the inherent trust placed in collaboration tools often overrides standard security instincts, granting threat actors a direct, high-trust channel to your end users.
Threat overview
The attack we’ve observed typically follows a specific sequence of events:
Initial contact: The threat actor sends spoofed Microsoft Teams chat requests to multiple users within an environment, simultaneously. These often appear to come from “IT Support,” “System Admin,” or other spoofed internal aliases.
Engagement: Once a user accepts the chat request, the threat actor initiates a conversation under the pretext of IT support offering computer support, such as “fixing a technical issue” or “performing a security update.”
Exploitation: The threat actor requests the user to launch Quick Assist. Once the connection is established, the TA gains remote access to the machine, allowing them to deploy malware, exfiltrate data, or move laterally through the network.
What you should do now
To protect your environment from this activity, Rapid7 recommends the following technical controls:
Harden Microsoft Teams settings
In the Teams Admin Center, limit external communications to “Only allowed domains.” This prevents random external tenants from messaging your employees unless they are on an approved allowlist. In addition, Rapid7 recommends disabling the ability for users to communicate with external Teams users who are not managed by an organization.
If your business doesn’t require cold outreach from external vendors, toggle off “Allow External Users to Start Conversations” to ensure only your users can initiate outside chats. If your business does require this functionality more broadly, consider implementing Spoof Intelligence.
Implement automatic blocking of spoofed Teams messages
Enable Spoof Intelligence within your Microsoft 365 security settings. This feature automatically detects and blocks senders who are not who they claim to be. This feature works by identifying and managing senders that fail SPF/DKIM/DMARC. If you have known senders who don’t have these configured, ensure you set the appropriate exceptions.
Disable/harden Quick Assist
Rapid7 recommends removing or disabling Microsoft Quick Assist if it is not required within your environment. This can be achieved via Group Policy Object (GPO) blocking the application, blocking network traffic to the Quick Assist domain, or uninstalling the Quick Assist package.
Watch for red flags
Train staff to recognize these specific “Teams spoofing” hallmarks:
The “external” tag: Remind users to look for the (external) tag next to a name. Real internal IT support will never have this tag.
Sense of urgency: Attackers often claim there is a “security breach” or “expired password” to rush the user into bypassing safety protocols.
Out-of-band verification: Establish a policy that IT will never initiate a support session via a cold-call Teams chat without a pre-existing ticket number. If a user is unsure, IT should have a pre-established process in place for a user to validate the requestor’s identity.
Rapid7 customers
We are continually monitoring your environment for related activity. Below is a non-exhaustive list of detections that are deployed:
Suspicious Chat Request – Potential Social Engineering Attempt
Suspicious Conversation – Potential Social Engineering Message Interaction
Initial Access – Potential Social Engineering Session Initiated Following Chat Request
Suspicious Chat Request – Multiple Users Contacted by Foreign Tenant via Default Tenant Domain
Initial Access – Microsoft Teams Remote Control Granted to Suspicious External Account
Rapid7 MDR is here to support your team, strengthen your defenses, and help you stay ahead of adversaries attempting to use this tactic to gain access to your environment. Learn more about our service here.
Detection and response are under pressure. Expanding attack surfaces, identity misuse, cloud sprawl, and AI-accelerated threats have changed what “ready” looks like for a SOC. That’s why this year’s Global Cybersecurity Summit places Continuous Threat Defense at the center of the conversation.
The focus is clear: this is what modern MDR looks like when it’s designed to disrupt attackers earlier, not just react to them faster.
2026 MDR sessions: A sneak peek
Throughout the summit, several sessions will explore how detection and response are evolving in practice. In this year’s “Inside the Modern SOC”, we’ll look at how response actually unfolds when pressure is high and decisions matter. It’s a close examination of ownership, escalation, and how teams coordinate across endpoint, identity, and cloud telemetry.
In “Using Red Teaming to Power Preemptive MDR”, the conversation shifts upstream. Rather than treating red teaming as a compliance exercise, this session examines how continuous testing strengthens detection coverage and validates response workflows before a real attacker forces the issue.
For the executive leaders “A CISO’s Guide to MDR Accountability and Outcomes” will examine MDR through a leadership lens, describing how leaders can best evaluate performance, define success, and ensure response strategies hold up under scrutiny. As detection models grow more complex, clarity around accountability can become just as important as technical capability.
For hands-on practitioners, “Hunt or Be Hunted: Frontline Tales of Detection” offers a scenario-driven walkthrough of how SOC analysts triage signals, manage handoffs, and make decisions under real operational pressure. Meanwhile,” IR in Practice: Tools, Tradecraft, and Adversary-Informed Investigation” provides a deeper look at investigative workflows, including practical use cases and adversary-informed response approaches.
What preemptive MDR really means
Together, these sessions represent part of a broader theme: Preemptive Security Operations is not about adding more tools or generating more alerts. It is about reducing uncertainty, aligning exposure with detection, and building workflows that allow teams to act with confidence.
And this is only a preview. Additional sessions, speakers, and perspectives will continue to be announced as the summit approaches.
If you’re responsible for detection strategy, response readiness, or MDR governance, this track is designed to meet you where you operate. Join us May 12–13 and be part of the shift toward more confident, preemptive security operations.
In 2025, we launched Experts on Experts: Commanding Perspectives as a pilot video series designed to spotlight the ideas shaping cybersecurity, directly from the people driving them. Over five episodes, Rapid7 leaders shared short, candid conversations on topics like agentic AI, MDR ROI, cybercrime-as-a-service, and policy in practice. With Season Two launching soon, now is the perfect time to revisit the first run of expert conversations that started it all.
Each episode is now embedded in its supporting blog on rapid7.com, making it even easier to watch, read, and share. Here’s your full recap of Season One.
Ep 1: What Happens When Agentic AIs Talk to Each Other?
Agentic AI was one of the most talked-about themes of the year, but few tackled it with the clarity and urgency Laura Ellis brought to this episode. From governance models to inter-agent deception, the conversation explores how AI systems can interact in unpredictable ways. Laura shares her perspective on keeping humans at the helm, how to contain agent behavior in real-world infrastructure, and what’s realistic for security teams today. The episode came from a LinkedIn conversation about autonomy, oversight, and the potential for agent-to-agent manipulation, and answered a lot of questions. If you’re curious about how AI moves from experiment to ecosystem, this is a great place to start.
Ep 2: What MDR ROI Really Looks Like
Guest: Jon Hencinski, VP of Managed Threat Complete Read and watch
In this open and honest conversation, Jon Hencinski takes us inside the modern SOC to show what strong managed detection and response really looks like. From coverage and telemetry to analyst training and noise reduction, the episode walks through the building blocks of a high-performing MDR program. Jon speaks directly to security leaders and decision-makers, breaking down which metrics matter most, how to measure confidence in your provider, and why speed is still the differentiator. If you’re evaluating MDR partners or trying to articulate the value of your program internally, this episode offers a practical benchmark. It also pairs well with Rapid7’s IDC report on MDR business value, which (Spoiler Alert) found a 422% three-year ROI and payback in under six months.
Ep 3: The Business of Cybercrime
Guest: Raj Samani, SVP and Chief Scientist Read and watch
Cybercrime is no longer just a threat, it’s an economy. In this episode, Raj Samani unpacks the business model behind ransomware, initial access brokers, and affiliate operations. He shares his view on how cybercriminals are scaling operations like startups, what security teams can do to map that behavior, and why understanding the economy of access is key to disruption. It’s an insightful look at how attacker innovation is outpacing the traditional response, and what needs to change. Raj also reflects on the blurred lines between opportunistic access and long-tail ransomware campaigns, and how buyers on the dark web shape the threat landscape. This conversation is especially useful for defenders who want to think more strategically about adversaries and the systems that support them.
Ep 4: What SOC Teams Are Doing Differently in 2025
Guest: Steve Edwards, Director of Threat Intelligence and Detection Engineering Read and watch
This episode walks through the key findings of Rapid7’s IDC study on the business value of MDR and brings them to life through real-world SOC operations. Steve Edwards shares how telemetry access changes the game, what true coverage looks like in practice, and why teams are shifting away from reactive models to faster, context-rich detection. You’ll hear what happens in the first 24 to 48 hours of incident response and how Rapid7’s no-cap IR model improves confidence during high-pressure moments. Steve also breaks down how teams are using MITRE ATT&CK mapping to prioritize security investments and measure response maturity over time. For security leaders and buyers evaluating managed services, this conversation offers a clear, practical lens on what a successful MDR program looks like from a security and business perspective.
Ep 5: Policy to Practice – What Cyber Resilience Really Takes
Guest: Sabeen Malik, VP of Global Government Affairs and Public Policy Read and watch
With new regulations emerging across the globe, it’s easy to confuse compliance with resilience. In this episode, Sabeen Malik unpacks what it takes to bridge that gap. She talks through disclosure laws, geopolitical tension, and the difficulty of turning policy into something operators can act on. Sabeen brings both policy expertise and operational realism, making the case that cybersecurity regulation needs to be built for the real world, not for a checklist. She also explores the cultural side of risk, including how insider threats and trust-based frameworks play into resilience planning. If your organization is tracking regulatory changes or working toward a more mature security posture, this episode offers a smart lens on where policy can help, and how to overcome it’s shortfalls.
Organizations increasingly rely on Microsoft as their foundational productivity and security technology provider. As these environments grow in scale and complexity, security leaders are responsible for operationalizing the vast signals traversing their Microsoft stack in order to anticipate and preempt threats. At the same time, those efforts must deliver measurable security outcomes and clear return on investment.
If you’re reading this, you already know what’s at stake. But I’ll say it louder for the folks in the back: As more of your environment consolidates onto Microsoft, the attack surface evolves – and without fully operationalizing that ecosystem, risk grows alongside it. We are excited to announce the availability of Rapid7 MDR for Microsoft – a preemptive threat detection, investigation, and response service that brings together Rapid7’s global SOC, our market-leading SIEM technology, and deeper bi-directional Microsoft Defender integrations. The service helps security and IT teams maximize their investments, reduce cost and complexity, respond decisively to threats, and improve their security posture and resilience.
Extend the power of your stack
Microsoft Defender provides broad visibility across modern environments – from endpoint and identity to cloud and email. That visibility leads many organizations to a fine line, where it can either mean rich, actionable insight for some security teams, and overwhelming signal volume and missed alerts for others. Rapid7 helps organizations build a clear picture from the rich telemetry by bringing these Microsoft signals together with our native telemetry. And by incorporating exposure and asset risk directly into investigations, our SOC is empowered to anticipate likely breach paths and intervene earlier in the attack lifecycle. Combining your Microsoft security stack with our preemptive MDR ultimately helps you:
Maximize the return on your existing Microsoft investments
Reduce the cost and operational burden associated with managing a SIEM
Gain the confidence that threats will be contained and neutralized
Improve the long-term posture and resilience of your security program
Capabilities that drive real-world outcomes
Leaning into Rapid7’s proven record as a leader in managed detection and response, MDR for Microsoft combines powerful AI-SOC technology with expert human service delivery to help Microsoft-centric organizations achieve measurable security outcomes. In IDC’s recent Business Value of Rapid7 MDR study, customers achieved a 422% three-year ROI, identified threats 87% faster, and reduced the likelihood of a major security event by 54%. MDR for Microsoft delivers these same results through capabilities designed to operationalize and protect Microsoft environments at scale, including:
Risk-aware analysis that stops attacks earlier: By pairing enterprise vulnerability risk management with analysis of live threat activity, the service preemptively identifies the attack paths most likely to be exploited – empowering efficient analyst evaluation with a clear understanding of underlying asset context.
Dedicated cybersecurity advisor extends your team: Your advisor leverages their practitioner experience to provide regular threat briefings, environment-hardening advice, program governance, and health checks – helping drive long-term maturity without adding headcount.
Decisive response backed by deep forensics and unlimited IR: Remote containment, endpoint forensics powered by our open-source DFIR framework – Velociraptor – and unlimited incident response ensure threats are stopped quickly, and fully investigated and neutralized before our team rests.
Unlimited log ingestion delivers predictable value: Remove SIEM cost constraints and ensure complete visibility so investigations are never limited by data volume or surprise overage fees.
Bi-Directional Defender integration that reduces friction: Endpoint alerts and analyst actions stay synchronized between Rapid7 and Microsoft consoles, keeping systems aligned while laying the foundation for broader integrations across additional Microsoft security vectors.
Always-on, expert-led SOC coverage: Our 24x7x365 global SOC continuously monitors and investigates activity across Microsoft and non-Microsoft environments, ensuring threats are identified and acted on as soon as they emerge.
Full transparency into SOC activity and outcomes: With direct access to the SIEM and investigation workflows, your team can ride sidecar on investigations, run your own queries, upskill internal teams, and clearly see the outcomes being delivered by the Rapid7 SOC over time.
Additional value-drivers included in the service are unlimited SOAR automation, standard 13-month data retention with the ability to extend, proactive threat hunting, and AI-assisted investigation workflows, delivering a comprehensive MDR experience that scales with your environment and outpaces attackers.
Make the most of Microsoft Defender with Rapid7
As Microsoft continues to serve as the backbone of modern environments, the ability to translate security signals into consistent action becomes increasingly critical. MDR for Microsoft is designed to help security leaders move confidently from visibility to outcomes – pairing the strength of Microsoft Defender with Rapid7’s proven expertise, preemptive risk-awareness, and resilience-building capabilities. The result is a security program that not only sees more, but responds faster, operates with greater confidence, and proves its value as environments continue to scale.
If you’d like to see how MDR for Microsoft can help you operationalize your Microsoft security stack, request a demo or reach out to your Rapid7 account team to continue the conversation.
Over the last six months we’ve delivered significant advancements across the Command Platform, as well as received recognition as a Leader in Exposure Management and Managed Detection and Response (MDR) analyst reports. From launching new AI-driven capabilities – including our new next-gen SIEM Incident Command – to introducing real-time visibility into organizational risk with enhanced dashboarding, we continued to innovate in ways that support faster, more confident decision making. Explore the highlights of what we’ve been up to below.
Exposure Management: Prioritize risk across your attack surface
Rapid7 named a Leader in the 2025 Gartner® Magic Quadrant™ for Exposure Assessment Platforms
Rapid7 was recognized as a Leader in the inaugural 2025 Gartner® Magic Quadrant™ for Exposure Assessment Platforms (EAP). We believe this reflects our ability to help customers continuously understand, prioritize, and reduce risk across their hybrid environments. Exposure Command brings unified visibility, attacker-aware prioritization, and guided remediation together in one platform, enabling teams to make faster, more confident decisions with validated, business-aligned risk insights. Check out our recent blog post to learn more.
Remediate vulnerabilities faster with AI-generated Risk Intelligence
Prioritizing remediation is difficult when teams are flooded with CVEs and lack actionable context about real-world risk. We introduced AI-generated risk intelligence within Remediation Hub to help teams focus on the vulnerabilities that matter most and drive faster, more consistent risk reduction by distilling exploitability, business impact, toxic combinations, and patchability into clear summaries and guided actions. Check out our recent blog post to learn more.
⠀
AI-generated Remediation Summary in Remediation Hub
Gain real-time visibility and communicate progress with the Exposure Management Dashboard
To effectively plan, track, and communicate exposure reduction, teams need a clear, real-time view of their security posture. The new Exposure Management Dashboard provides this view with an at-a-glance snapshot of asset coverage, exposure trends, and remediation progress — ideal for quarterly planning cycles and board-level reporting. Exportable views make it easy to justify investment decisions, demonstrate measurable improvements, and show how tool consolidation is strengthening your security program. Learn more in our recent blog.
⠀
Exposure Management Dashboard, built to give you a real-time view of organizational risk
Validate real cloud exposures with Public Exposure Validation
When cloud configurations drift or controls degrade, it’s critical to know which assets are actually exposed to the public internet. Public Exposure Validation confirms externally reachable cloud resources using real external scans, reducing noise and eliminating theoretical findings.
Teams gain clearer visibility into true attack paths, shorten investigation cycles, and validate that remediation efforts are closing real gaps. This strengthens their posture with evidence, not assumptions. Learn more in our recent blog.
Keep external visibility accurate with Dynamic EASM Discovery
Accurate external discovery depends on seeds that reflect what’s truly exposed. But static seed lists can quickly become outdated. Dynamic EASM Discovery continuously pulls domains and public IP ranges from authoritative sources such as MarkMonitor, NetBox, and Rapid7 AppSec, ensuring your discovery scope stays current without manual upkeep.
This eliminates blind spots, keeps external inventories aligned with real-world change, and strengthens CTEM outcomes by grounding scope, discovery, and prioritization in real-time data rather than spreadsheets. See our recent blog on Dynamic EASM Discovery to learn more.
Detection and Response: Transform your SOC operations
Rapid7 named a Leader in the 2025 Frost Radar™ for Managed Detection and Response
In addition to being named a Leader in Exposure Assessment, we’re proud to share that we have also received this recognition for Managed Detection and Response with Frost & Sullivan recognizing Rapid7 as aLeader in the 2025 Frost Radar™ for MDR, based on innovation and growth in a field of 120 evaluated vendors. The report highlights:
Rapid7’s AI-driven triage accuracy of 99.93%, which helps security teams close benign alerts and reclaim 200+ SOC hours per week
Our unified platform combining MDR with exposure management, threat hunting, and active remediation
180+ third-party integrations across endpoint, network, cloud, and identity
This recognition reinforces Rapid7’s commitment to proactive, outcome-driven security and delivering continuous innovation, transparent AI, and measurable value to customers. Learn more.
IDC publishes its Business Value of Rapid7 MDR Study
IDC recently published its Business Value of Rapid7 MDR study, highlighting how customers can achieve a 422% three-year ROI, a 5-month payback period, and an impressive range of additional security outcomes delivered through Rapid7 Managed Detection and Response. The study found that Rapid7 MDR significantly reduced the chances of major security incidents and improved the speed to identify threats for customers – translating to both risk reduction and cost savings. Learn more about the study in our blog or download the full report.
New third party event sources available for Rapid7 SOC management
For organizations to stay secure, they need visibility across their entire attack surface. With recent third party event source expansions, our Rapid7 SOC can now manage PAN Cortex XDR, Okta Identity, and Google Security Command Center alerts as a part of our MDR and Managed Threat Complete offerings. This reinforces our defense-in-depth approach, in which Rapid7 collects, correlates, and maps native and third party telemetry to the MITRE ATT&CK framework, providing expanded visibility and greater protection across your entire attack surface. Learn more about SOC-supported third-party event sources here.
Introducing Incident Command
In July we announced our new AI-powered, next-gen SIEM, Incident Command. Designed to transform how security teams manage investigations and response, Incident Command automates manual tasks and guides analysts through complex workflows — accelerating triage, providing real-time recommended actions, and unifying critical context across alerts and incidents.
Backed with generative AI, our next-gen SIEM helps teams reduce mean time to respond (MTTR), improve consistency, and scale security operations without adding headcount. Learn more about what Incident Command can do for your team here.
⠀
The Incident Command Home Page brings critical SOC analyst tools together into a singular, actionable view
Rapid7 recognized for the 7th consecutive year in Gartner® Magic Quadrant™ for SIEM
Rapid7 has been recognized in the 2025 Gartner® Magic Quadrant™ for Security Information and Event Management (SIEM), proof of our continued focus on helping security teams work smarter, respond faster, and stay ahead of evolving threats. This year’s report explores how SIEMs are transforming to meet the demands of modern, hybrid environments with greater automation, stronger analytics, and improved efficiency across security operations. We believe our inclusion underscores our commitment to delivering speed, transparency, and extensibility with our next-gen SIEM. Read the report for more insights.
InsightGovCloud: Trusted security for federal agencies
Rapid7 achieves FedRAMP authorization for InsightGovCloud platform
Our achievement of FedRAMP Authorization to Operate (ATO) underscores our commitment to delivering secure, trusted cloud security solutions for federal agencies. The InsightGovCloud Platform provides government customers with vetted capabilities for vulnerability management, cloud security posture, and threat detection, meeting the rigorous standards required to protect sensitive federal environments, while enabling faster, more efficient security operations. Learn more.
Rapid7 Labs: Uplevel your defenses with our latest cybersecurity intelligence and research findings
New research: Q3 2025 Threat Landscape Report
Our Threat Landscape Report provides an analysis of global adversary behavior drawn from Rapid7’s MDR operations, vulnerability intelligence, and threat research. Our latest Q3 2025 report outlines key trends that are shaping today’s threat environment – including AI-assisted attacks and the rapid operationalization of new vulnerabilities – offering clear guidance to help security teams anticipate emerging risks and strengthen defenses in an increasingly fast-evolving landscape. Read the report here.
Emergent threat response: Real-time guidance for critical threats
Rapid7’s Emergent Threat Response (ETR) program from Rapid7 Labs delivers fast, expert analysis and first-rate security content for the highest-priority security threats. In H2 2025, Rapid7’s ETR team provided expert analysis, content, and mitigation guidance for a variety of notable vulnerabilities, including:
CVE-2025-10035: Critical unauthenticated RCE in GoAnywhere MFT
CVE-2025-53770: Zero-day exploitation in the wild of Microsoft SharePoint servers
Follow along here to see the latest emergent threat guidance from our team.
Technical assessments of CVEs in AttackerKB
Rapid7 researchers also publish additional vulnerability assessments in AttackerKB to help customers and the community understand and prioritize notable CVEs. Notable contributions from the back-half of 2025 include:
CVE-2025-12480 – Gladinet CentreStack RCE via access control bypass
Stay tuned for more!
As always, we’re continuing to work on exciting product enhancements and releases throughout the year. Keep an eye on our blog and release notes as we continue to highlight the latest in product and service investments at Rapid7.
Across industries, Microsoft is everywhere. It powers productivity, collaboration, and security through Defender, Sentinel, Entra, and the broader Microsoft ecosystem that underpins how modern organizations operate.
⠀
As organizations deepen their Microsoft investments, there’s an even greater opportunity to strengthen and simplify threat detection and response. Microsoft delivers powerful visibility and security insights across user identities, endpoints, and cloud workloads, but security teams often need help bringing those capabilities together with the rest of their environment to ensure that data, detections, and decisions that drive their threat detection and response program align seamlessly.
⠀
That’s where Rapid7 comes in.
⠀
A shared vision for simplified, unified security
We’re excited to announce the launch of an expanded partnership between Rapid7 and Microsoft, focused on helping organizations fully realize the potential of their Microsoft security investments. Together, we’re building a unified approach to threat detection and response that combines Microsoft’s ecosystem and scale with Rapid7’s AI-native security operations platform and decades of SOC expertise.
⠀
Our shared goal: help customers protect their businesses with clarity, speed, and confidence.
⠀
For many organizations, Microsoft is the backbone of their IT and security programs. But it’s only one part of a larger, interconnected environment. Security leaders need a way to bring Microsoft Defender, Sentinel, and Entra data into context with the rest of their infrastructure, cloud, and SaaS investments. Rapid7 helps make that possible by connecting Microsoft’s advanced telemetry and analytics with broader visibility and context into all security data, automation, and 24/7 expert-led managed operations.
⠀
We’ve long incorporated deep Microsoft visibility across the Command Platform, integrating with tools across different use cases, such as attack surface management, exposure management, cloud security, and application security. This foundation already allows us to correlate insights across on-premises and cloud environments, including Active Directory, Azure, and Microsoft 365 – providing outcomes across endpoints, workloads, and applications. These capabilities unify context from more than a dozen different Microsoft and Azure tools, giving customers a complete picture of risk across their environment.
⠀
This partnership combines Microsoft Defender’s signal depth with Rapid7’s threat intelligence, automation, and human-led operations to deliver complete visibility and coordinated response across your environment – from Microsoft to everything it touches.
⠀
This means:
Unified security operations managed for you: Rapid7 delivers 24×7 monitoring, investigation, and response across Microsoft and non-Microsoft environments, combining Defender insights with our own detection and response workflows to act quickly on what matters most.
Faster, smarter response: AI-driven correlation and human-led expertise reduce alert noise and accelerate containment when threats arise.
Simplified, predictable operations: Our managed detection and response (MDR) service removes ingestion complexity so you can focus on security outcomes.
Transparency and trust: Built in through seamless integration with the Microsoft consoles security teams already use.
⠀
A foundation for what’s next
Over the coming months, we’ll introduce new capabilities that make it easier for customers to operationalize Microsoft security within the Rapid7 ecosystem, including unified MDR coverage across the Defender products that protect the key vectors of endpoint, identity, cloud, and email.
⠀
These enhancements will enable organizations to not only respond to Microsoft-based threats faster but also proactively reduce risk across their entire environment through unified detection, investigation, and response.
⠀
We’re excited for this next step in advancing our MDR services to meet Microsoft customers where they are and maximize their investments with comprehensive visibility, faster response, and measurable security outcomes.
⠀
We’ll be releasing more information soon. In the meantime, learn more about Rapid7’s leading MDR service here.
Cybersecurity ROI is notoriously difficult to define, but not impossible.
In this Experts on Experts: Commanding Perspectivesepisode, Craig Adams chats with Steve Edwards, Director of Threat Intelligence & Detection Engineering, about what customers really get from Rapid7 MDR and how to think more clearly about value.
They cut through buzzwords and talk real-world outcomes: visibility, consolidation, faster response, and trust.
What ROI really looks like
As Steve explains, the ROI conversation starts with confidence. Once customers know they can trust the MDR team to cut through noise and take action, the benefits snowball from reduced false positives, to better visibility and smarter spend.
The IDC study highlighted a 422% ROI over three years. But the real signal is what teams can do with the time and clarity they gain.
To bring these numbers into your own context, you can use the Rapid7 MDR ROI Calculator – simply plug in your own parameters and apply IDC’s methodology to estimate your unique return. Try the ROI Calculator!
Telemetry without tradeoffs
Craig and Steve also dig into one of the biggest detection challenges today: partial visibility. Many orgs still pay by the log, creating disincentives for full data ingestion. MDR’s all-in access model helps customers detect threats earlier and act faster, without needing to triage upstream data decisions.
MITRE mapping makes it click
One of the most actionable insights? MITRE mapping. Steve talks about how customers are using visual coverage data to pinpoint gaps and prioritize onboarding new tech, or building compensating controls.
No-cap incident response
They also walk through what happens during the first 24 – 48 hours of an incident, and why having no cap on IR hours means Rapid7 can stay involved from containment to eradication.
Missed our earlier episodes? Catch up on Episode 1 with Laura Ellis on agentic AI and system governance [here], Episode 2 with Jon Hencinski on MDR strategy and SOC readiness [here] and Episode 3 with Raj Samani on cybercrime-as-a-service [here]
The collective thoughts of the interwebz
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.