Tag Archives: Featured-Backing Up

Let’s Not Go Phishing Today: Tips for Home Computer Users

Post Syndicated from original https://www.backblaze.com/blog/lets-not-go-phishing-today-tips-for-home-computer-users/
Every so often, a family member or friend will ask me if an email they received is a phishing email. That’s part of my job as the unofficial family tech person. Email phishing and its cousins vishing (voice phishing) and smishing (text phishing), are still a serious problem for the average home computer user. While businesses are slowly implementing phishing detection tools—and, more importantly, user training—to help tackle the problem, home computer users are, for the most part, left to fend for themselves.

Our goal in this post is to provide a few tips and tricks for those oft-forgotten home computer users—your old-school neighbor, your unassuming grandma, or your friend who’s just not that tech savvy—in their effort to use their computer without losing their life savings by clicking on the wrong link.

You can scroll past the first few sections to the phishing tips we’ve prepared so that you can use to better understand and identify a phishing email. Or, continue reading to learn more about the phishing problem, why it matters, and then finish up with the phishing tips.

Why It Matters

Phishing is the use of social engineering techniques—tactics that use psychological manipulation like impersonating someone you know—to get you to take an action that can lead to your downloading a virus or malware, having your account credentials stolen, becoming an extortion victim, or some other malicious action.

While detection and blocking technology has advanced over the years, Dark Reading, a cyber security news site, estimates that up to one percent of all emails that make it to the end user’s mailbox are phishing emails. For home users, who typically have to rely on their internet service provider (referred to as an ISP) or their browser (like Chrome or Safari) to keep them safe, the number is probably higher. Still, 1% doesn’t sound like much—until you consider that to get to that point, these phishing emails are the best of the best. Suddenly, it starts to make sense as to why up to 70% of phishing emails are opened by the recipient.

Who Owns the Phishing Problem?

My friends and family are not creators or purveyors of technology; they are primarily users. Asking them to identify phishing emails by deciphering the email raw source or header is not in their wheelhouse, nor should it be. We take planes, trains, and automobiles without knowing much about how they work. It should be possible to safely receive and interact with an email without having to understand sender authentication or bone up on RFC 5322.
You as the family IT manager.

Back in 2005, when most of us first heard of phishing, we had a pretty good idea which businesses and people would contact us and how they would reach us. Today, nearly every company or organization we interact with has a website, an email subscription, an app, social media, and maybe a phone number or two. The daily number of messages we receive via email, phone, text, and so on has easily increased 10-fold (100-fold?) over that time. Do you really have any idea how many accounts you’ve created in your lifetime, and if so, how each of them reaches and interacts with you?

Making matters worse is the proliferation of data collection services—legitimate, shady, and illegal—which will sell personal information to nearly anyone with a purchase order, credit card, or better yet, the latest cryptocurrency. Personal data such as your name, address, last four digits of a credit card, and much more are readily available. As a result, a phishing email can use your name and provide additional personal details along the way in an effort to make you believe it is valid ← that’s social engineering at work.

What Can You Do?

For home computer users, the phishing problem may not be of your making, but you cannot rely on technology if you want to safely function in today’s highly connected world. Phishing uses some really crafty tactics (i.e. social engineering) to get you to believe that when you receive a message from the bad guys, it is okay to do what they are asking you to do. That means you have to be at your best when the incoming message chime rings.

To that end, below we’ve provided you with a little social engineering education in the form of some easy to remember tips you can use to ferret out a phish. We’ll use email in our examples, but the techniques can apply to most inbound communications you’ll receive. In addition, you don’t have to have any special technical superpowers, just some common sense and the ability to lower your FOMO (fear of missing out) threshold.

You can read the tips below, but we’ve also prepared a 20-minute Let’s Not Go Phishing Today webinar which provides a little more depth for each of these tips. You can read the tips below, watch the webinar, or both. The webinar is available on the Backblaze channel on BrightTALK. Keep in mind that you will need to register to watch.

Tip 1: No trust and not useful.

Situation You receive an email from a business, organization, or person. You are certain you do not know or trust the sender and you were not expecting to receive the email.
Example You receive an email to lower your mortgage interest rate from a bank you do not use. Oh, and you rent.
Considerations There are zero reasons to open this email. There is no upside here at all for you. Even if this is not phishing, it is most likely spam.
Disposition Delete the email while crooning, “But there ain’t no Coupe de Ville hiding at the bottom of a Cracker Jack box,” in the style of Meat Loaf (“Two Out of Three Ain’t Bad,” Bat Out of Hell, 1977).

Your on-stage moment is at 2:27.

Tip 2: No trust, but you’re not sure.

Okay, tip one was pretty simple. They get a little harder now.

Situation You receive an email from a business, organization, or person. You might know the sender, but you really weren’t expecting an email.
Example You receive an email and the sender name sounds familiar, but that’s it. Maybe you stopped by a store and provided your email to the clerk, maybe you bought a shirt from them two years ago, or maybe it’s just some advertisement you saw, but nothing is ringing a bell.
Considerations
  • Don’t open the email right away, let it sit in your inbox for a day or two to see if there is a follow up message or perhaps you remember something.
  • Often phishers will use time to pressure you into acting. Surely you would have remembered something so important, so don’t let time pressure you into doing something you shouldn’t. Trust yourself.
  • If you do open the email do not click on any of the links and do not call any phone numbers you may find in the email. Just read the email to see if anything jogs your memory.
Disposition
  • After a day or two, if nothing rings a bell, delete the email. If it was important, they’ll resend. Click delete.
  • If you think the email could be legit—Okay, really, just lower your FOMO threshold and click delete. I am sure that a bank in Ireland is not waiting to give you a million dollars if you call them.

Fun fact: $1 million in $1 bills weighs 1.1 tons. Say that three times fast!

Tip 3: Trust, but verify.

Situation You receive an email from a business, organization, or person. You know the sender, but you weren’t really expecting an email from them.
Example You receive a promotional email from a business. You are a customer of this business and even have an online account with them. You were not expecting the email, but the email makes you an offer that is interesting to you.
Considerations
  • You can receive promotional emails anytime, but they are more prevalent around holidays and marketing events like Cyber Monday. Phishers know this and will use this to their advantage to avoid detection.
  • A phisher can send out millions of emails in an attack spoofing a given business. If you have a relationship with that business, you are prime pickings. Do not assume that just because you are a customer, the email is legitimate.
  • A phisher can also send out very targeted emails using personal information they have collected from data breaches and other sources, both public and private. Just because an email has your name and other personal details, it does not mean it is legitimate.
  • If you decide to open the email do not click on any of the links and do not call any phone numbers you may find in the email. Read the email and see what they are asking you to do.
Disposition
  • If you think the promotional offer is legitimate, then open a new browser window and type in the URL to go to the website, or open the app on your phone/tablet for that business. You may have to sign in to your account, but the promotion should be available in one of those places. If the promotion is only available via the email, contact customer service for the business and ask. Remember to use the website or app to contact customer service, not any of the contact information provided in the email.
  • Sometimes, an offer is only available by clicking on a link in the email. In my opinion this is lazy marketing and puts you at risk. Let the business know this is not acceptable.

Spam or Phish?

The email described above could be just a spam email. Whether an email is spam or phishing can be confusing, but in general spam messages are just trying to sell you something and phishing emails have some harmful intent. That said, the same tips we are using for identifying a phishing email can be used to identify spam messages as well.

Tip 4: Trust, but still verify.

Situation You receive an email from a business, organization, or person. You know the sender and you were expecting the email.
Example You receive an email on the 10th of the month from your credit card company saying your statement is ready. They always send you this email on the 10th of the month. The email says you can click on the link to sign in to your account and view the statement.
Considerations
  • It is highly likely this is a legitimate email, but given this email concerns your financial affairs, being extra careful is imperative. Opening up a web browser and typing in the URL to go to the bank’s website to sign in there is safer. This also enforces the good behavior of not clicking on links in emails.
  • Many financial companies and health care providers are starting to maintain a list of messages they send you via email and/or text. You can log into your account to view the list to make sure that any message you received was actually sent by the provider—before you interact with the message. This is an excellent best practice and such businesses should be commended for thinking about their customer’s online safety and security.
Disposition Even if you think the email is legitimate, use a web browser to access your online account, or use their app to take the requested action.

Downloading Email Attachments?

Only download an attachment that you were expecting to receive, preferably after you were notified via another email—or better yet another method such as a text message. For example, you or whomever you’re interacting with may say, “Hey Monique, I’m going to email those pictures in a minute.” Downloading unsolicited or unexpected attachments is not recommended.

Think of email, text messaging, and voicemail as read-only services, especially when it comes to your financial and health information. This is sometimes really hard with text messages that encourage you to “click this link to…” and voicemail messages saying “call us back at a specific number.” Such messages offer convenience and help move things forward—and sometimes, they are the only way to get things done. At that point, you have to trust the vendor and your instincts.

What to Do When You’re Forced to Click

There are two common situations where you are forced to click a link in an email or message in order to move forward: email newsletters and two factor (2FA) or multifactor (MFA) authentication.
We’re this happy about 2FA security too.

Newsletters

Newsletters can deliver valuable information and often link to other content for additional details. The trouble is, those links are often obscured by tracking redirects used to count how many clicks the link gets—It’s a marketing thing. The average user has little hope of figuring out where the link is actually going, so they are faced with ignoring the information or clicking to the unknown. Let’s break down an example.

Situation You receive a newsletter from a company you do business with and have received newsletters from them before.
Example Backblaze sends you a customer newsletter. There’s an article on a new feature and you want to learn more. To do so you have to click on a link, but when you rollover the link (don’t click) it reads something like:
“https://hub.backblaze.com/xxt/XXt/R+000/xx-h-99/V88XHdW7_bXrN4b0ml7W7xsyK94Tmm-9N2x86z13q3phV1-WJV7CgHCJW7swZm-8j6kXwW6cD…” plus 50-60 more characters that are not displayed.
Considerations
  • It may seem it goes to the Backblaze website (backblaze.com), but without seeing the entire URL you can’t be sure. It could end with “.../bad-guys-website.com“, which would not take you to Backblaze.
  • Were you expecting this newsletter or at least have you gotten a newsletter from Backblaze before? If it is the first time, did you just sign up?
  • What is the intent of the newsletter? Providing information or asking for something? If the newsletter is asking you to sign in to your account for example, it is easy enough to open a new web browser window and sign in from there.
Disposition
  • This one is all about trust, timing, and clicks. Let’s assume you trust Backblaze as a good sender, the newsletter looks very Backblaze-y, and this is something you would expect. If you do click on the newsletter links, there are two primary things to consider.
    • First, if the link takes you to a sign up or sign in page, stop. Always open a new browser window, enter the URL to go to the site, and sign in from there.
    • Second, make sure the click takes you where you expected to go. If you get pop-ups for downloading a toolbar or extension, land on an unexpected webpage, or other unusual browser behavior (e.g. an automatic download), close the browser window and everything else on your system. Then, run a full antivirus scan immediately.
  • If you are not inclined to click on any links in newsletters, we understand. In our case most of the links on a Backblaze newsletter will go to our blog or our website. You can open a new browser window and find the content on the Backblaze website. This works for the many different newsletters you may get daily. That is: You can usually find the content directly versus clicking on the link.

Tell Us More…

The problem with not clicking on the links in newsletters and other similar communications is that marketing folks lose information about what is important to the recipients, but your peace of mind is more important. So, a healthy alternative is that you could send an email or post something on social media about what you like and what you don’t. Even visiting the pages and interacting with the articles the newsletter highlighted will help. Marketers get feedback, you give your opinion on good content, and you’re a little safer from phishing attacks.

2FA or MFA

More and more websites are requiring the use of two factor or multifactor authentication. Here are a couple of scenarios to help you deal with the messages you might receive.

Scenario 1

Situation Your bank’s website uses text message-based two factor authentication to confirm access to your accounts.
Example Using a browser, you log in to your bank’s website. A couple of seconds later, you receive the text on your phone with a code that you need to enter on the website.
Disposition By asking to log in to your bank, you expect to get the text which provides the authentication code. You’re good.

Scenario 2

Situation Your bank’s website uses two factor authentication to confirm access to your accounts. You believe it is text message-based authentication.
Example Using a browser, you log in to your bank’s website. A couple of seconds later, you receive an email asking to click a link to allow the log in to your account.
Considerations
  • This is one of those cases where you need to know how the bank will contact you for the second factor. It could be a text message with the code (like the first example above). It could also be by clicking the link in a test message, or through an authentication app on your phone, or by email message, or even by phone.
  • Given the timing of the events in this example, it is highly likely that you had set up email as your second factor. But, sometimes it is not that easy to tell, especially if there are several minutes before you get the authentication message—or worse, if you don’t get the message at all.
  • One way to make this easier on you is to try to use the same authentication method for each website. The trouble is that different companies support different methods and not others. In some cases, you may be able to find information on the bank’s website to determine the authentication method they use.
Disposition If you’re not sure of the authentication method that was set up, you can abandon the sign-in, then open a new browser window and start again. If you get the same authentication method, you can be reasonably confident you’re doing the right thing.

Moving Forward

Over the past couple of years, vendors involved with providing email, text, and voicemail services have gotten better at detecting and eliminating phishing, spam, and malware before it reaches you. That’s great. But the bad guys haven’t given up, and many would say they’ve gotten better.

These tips are a good starting point for improving your ability to stay safe using the internet, email, and your phone. There are many websites and resources where you can learn more and stay informed about phishing and other forms of malware. We listed a few below. You can click on the links, but (if you are a little paranoid at this point), you can search for “consumer phishing resources” or just “phishing resources” using your favorite search engine. Good luck, and stay safe.

Select Phishing Resources

  1. Knowbe4: The world’s first and largest new-school security awareness training and simulated phishing platform.
  2. Phishing.org: A project from KnowBe4 that is a resource for IT professionals to keep you up to date on the latest phishing threats. The Resources page has some free tools to help improve your phishing knowledge.
  3. Phishing info from the Federal Trade Commission.
  4. A phishing primer from the National Cybersecurity Alliance.

The post Let’s Not Go Phishing Today: Tips for Home Computer Users appeared first on Backblaze Blog | Cloud Storage & Cloud Backup.
How to Download and Back Up Your Twitter Account

Post Syndicated from Barry Kaufman original https://www.backblaze.com/blog/how-to-download-and-back-up-your-twitter-account/

If you’ve been following the news lately, you might be thinking now is a good time to start downloading and backing up your Twitter history.

It’s officially the Elon Age of Twitter, and subsequently, there have been a few people rumbling about leaving the platform following Musk’s firing of top executives and an alarming rise in hate speech. Needless to say, we’re sticking around—you might have stumbled upon this article from Twitter itself. We just can’t quit the little blue bird quite yet. But there is one thing we can do, and that’s help you download and back up your Twitter archive—most likely for free.

Whether you’re anti-Elon or you’re just worried that the folks who are good at building electric cars or spaceships might not know how to manage a social media algorithm, you can take a few easy steps to protect your treasured Twitter memories. Here’s how.

Downloading Your Twitter Data

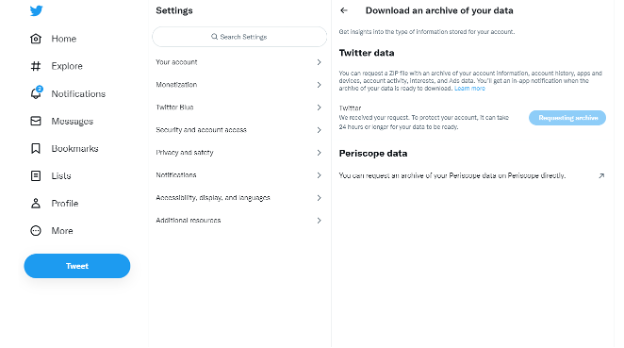
The first step is to log in to your Twitter account on a web browser. Once logged in, click on the “More” section in the navigation bar. From there, a new navigation bar will appear. You should select the “Settings and Support” dropdown, followed by the “Settings and Privacy” tab to progress.

Under the “Your Account” section, you will find an area labeled “Download an archive of your data.” The function of this is pretty self-explanatory, but does lead to a further menu that allows you to request an archive of your Twitter data or Periscope data.

After requesting your archive you will receive a notification with a link when your archive is ready for download. This archive will consist of a ZIP file with data that Twitter has deemed most relevant or useful to you, including DMs, moments, profile media and any media you may have used in your Tweets such as gifs, photos, and videos.

Archive Your Twitter Data for Free

Once you download your Twitter data, you can then save a full archive copy in the cloud on Backblaze B2—for free if it’s under 10GB.

Click here to get started with Backblaze B2 Storage Cloud today.

Back Up Your Twitter Data (Not Free, But Super Easy)

In addition to an archive copy, it’s important to use a secure backup strategy so all of those Tweets and memories will be preserved and kept safe from accidental deletion, equipment failure, or disasters (whether they’re natural or Musk-made). This is where a 3-2-1 backup strategy comes in handy. Using a 3-2-1 approach means keeping one copy of your data locally, one copy on a different type of media like an external hard drive, and one off-site (the cloud is a great place to keep it!).

You’ll need to manually download your Twitter data periodically, but once you have it on your machine, you can ensure it’s backed up with Backblaze Computer Backup—it automatically backs up all of your files, including documents, photos, music, movies, and, yes, all of that Twitter data you downloaded.

Click here to sign up for a 15-day trial of Backblaze Computer Backup, and save those Tweets.

While You’re At It…

We’ve gathered a handful of guides to help you protect social content across many different platforms. We’re working on developing this list—please comment below if you’d like to see another platform covered.

The post How to Download and Back Up Your Twitter Account appeared first on Backblaze Blog | Cloud Storage & Cloud Backup.
The 3-2-1 Backup Strategy

Post Syndicated from original https://backblaze.com/blog/the-3-2-1-backup-strategy/

A lot has changed since the 3-2-1 backup rule was first introduced in the late aughts. At the time, the iPad was just a glimmer in Apple’s eye. Facebook had a quaint 500 million users. Taylor Swift had only released two albums. Blockbuster Video still existed, and Netflix shipped DVDs to your door. 

Unlike most things in technology, the rule has held up over the years. It’s still the de facto standard for keeping your data safe. But some of the particular best practices have evolved as data storage has changed. Today, I’ll explain the 3-2-1 rule, what’s changed, and how you can easily achieve a 3-2-1 backup to keep your data safe and protected.

What Is the 3-2-1 Backup Rule?

The 3-2-1 backup rule is a simple, effective strategy for keeping your data safe. It advises that you keep three copies of your data on two different media with one copy off-site. Let’s break that down:

  • Three copies of your data: Your three copies include your original or production data plus two more copies.
  • On two different media: You should store your data on two different forms of media. This means something different today than it did in the late 2000s. I’ll talk a little more about this in a bit.
  • One copy off-site: You should keep one copy of your data off-site in a remote location, ideally more than a few miles away from your other two copies.

If you want to protect your personal information, photos, work files, or other important data, the 3-2-1 backup strategy is the way to go. It helps you avoid having a single point of failure that’s vulnerable to human error, hard drive crashes, theft, natural disasters, or ransomware.

How Does the 3-2-1 Backup Rule Work?

Let’s say you took a picture of your social security card for your tax accountant years ago—that file is called “socialsecurity.jpg” and it lives on your computer at home. That’s the first “copy” of your data.

You also have an external hard drive at home, used to back up your go-to Mac or gaming PC.  That external hard drive will back up socialsecurity.jpg as part of its backup process. That’s a second copy on a different device or medium.

In addition to that external hard drive, you also have an online backup solution (we recommend Backblaze; go figure!). The online backup continuously scans your computer and uploads your data to the cloud (which, in layman’s terms, is an off-site data center). Socialsecurity.jpg is included in this upload, becoming the third copy of your data.

Oh! And, your paper social security card is hopefully stored in a fire-proof safe (not your wallet) as a bonus. 

What’s Changed About the 3-2-1 Backup Strategy?

When the 3-2-1 rule was first introduced, there were a lot more types of media to choose from when storing your data—the humble floppy disk, CDs, Blu-ray discs, USB sticks, external hard disk drives (HDD), solid state drives (SSD), network attached storage (NAS), tape libraries, etc. Some of those have fallen out of favor (CDs and DVDs, I’m looking at you).

Some types of media are not practical or affordable for a typical home computer user looking to back up their data (tape libraries, for example). Some of the technologies were prohibitively expensive back then, but are much more affordable now (SSDs). And one big one wasn’t mainstream yet: The Cloud™ (you might have heard it referred to as “other people’s computers”). So, what does this mean for the 3-2-1 backup strategy? Do you still need to keep your data on two different media?
Two Different Media, Really?

The short answer is: yes, but no. Today, you don’t need to keep your data on two different types of media, but you do need to keep your data on two different devices. 

The long answer is a bit more complicated. There are a couple reasons folks recommended keeping your data on two different types of media in the first place. One, it protects you from one of those forms of media becoming obsolete in the face of new storage technology (still looking at you, CDs) and your data becoming unreadable. And two, it’s wise to keep your backup copy on a separate device so that a hardware failure doesn’t take out both local copies. For example, if your computer all of the sudden doesn’t want to hold a charge, you can still recover data from your hard drive.

While obsolescence is always a concern, the advent of cloud storage for backups all but eliminates it. The cloud service provider is responsible for maintaining the physical storage devices and keeping your data accessible at all times. So, if you use a cloud backup service, you only need to worry about keeping your data on two devices, not two separate kinds of media. What does that look like? 

The Easiest 3-2-1 Backup

If you back up your home computer to an external hard drive and back both of those devices up to the cloud using something like Backblaze Computer Backup, congratulations: You have achieved a 3-2-1 backup. 

  • You have three copies of your data: One on your computer, one on your hard drive, and one in the cloud.
  • You store your data on two different devices: Your computer and your external hard drive. (Technically, three devices, since your data is also stored in the cloud).
  • One of those copies is off-site: The cloud copy.

Is the 3-2-1 Strategy Still the Standard?

If you aren’t backing up at all, achieving a 3-2-1 backup strategy is still the best thing you can do to protect your data. But, the 3-2-1 rule is becoming more of a starting point rather than the finish line in today’s world. 

The rise in ransomware attacks calls for strengthening the basic principles of the 3-2-1 strategy—redundancy, geographic distance, and access—with added protections. Cybercrimes targeting networked machines and capturing all data, including backups, is a growing problem.

New versions of the tried-and-true backup strategy have emerged, such as the 3-2-1-1-0 or 4-3-2 backups. Sounds like overkill? It isn’t. The good news is that companies like Backblaze exist to make at least the off-site component less stressful—we do the work and keep up with security best practices for you.

Why Do I Need Both an On-Site and an Off-Site Backup?

Whether you are interested in backing up a Mac or a PC, an on-site backup is a simple way to access your data quickly should anything happen to your computer. If your laptop or desktop’s hard drive crashes, and you have an up-to-date external hard drive available, you can quickly get most of your data back or use the external drive on another computer while yours gets fixed or replaced. If you remember to keep that external hard drive fairly up to date, the exposure for data loss is negligible, as you might only lose the uncopied files on your laptop. Most external hard drives even come with software to ensure they’re readily updated.

Having an on-site backup is a great start, but having an off-site backup is a key component in having a complete backup strategy, including cloud storage. The newer backup strategies build on the cloud’s strengths:

  • Convenience: Backing up large volumes of data in the cloud is fast.
  • Durability and reliability: Your data is protected against fires, natural disasters, and more.
  • Collaboration: Sharing with permissions is intuitive and effortless in the cloud.

Is the 3-2-1 Backup Rule Perfect?

There is no such thing as a perfect backup system, but the 3-2-1 approach is a great start for most people and businesses. Even the United States government recommends this approach. In a 2012 paper for the United States Computer Emergency Readiness Team (US-CERT), Carnegie Mellon recommended the 3-2-1 method in their publication: Data Backup Options.

Backing Up Is the Best Insurance

The 3-2-1 plan is great for getting your files backed up. If you view the strategy like an insurance policy, you want one that provides the coverage needed should the unthinkable happen. Service also matters; having a local, off-site, and offline backup gives you more options for backup recovery.

Backblaze Backup in 3-2-1…

While Backblaze can’t help with power outages, computer encryption, or anti-theft technologies (though we can locate a computer), we can help make backing up your files a no-brainer. And (at least to our most recent survey) with only 11% of respondents who own a computer backing up daily, folks need the help!

Getting started with Computer Backup for your personal or business computers helps take care of that crucial “1” in your complete 3-2-1 backup strategy. And, with our included one year Version History feature (or Forever Version History if you want to upgrade), you have additional layers of protection should anything happen to your physical devices.

The post The 3-2-1 Backup Strategy appeared first on Backblaze Blog | Cloud Storage & Cloud Backup

Getting Rid of Your PC? Here’s How to Wipe a Windows SSD or Hard Drive

Post Syndicated from Molly Clancy original https://www.backblaze.com/blog/how-to-wipe-pc-ssd-or-hard-drive/

A decorative image showing a PC and a hard drive over a cloud.

Do you have an old PC lying around that you’d love to throw away or donate? Before you take it to the recycling center, you definitely want to scrub it of all your data. And there’s a bit more to it than just deleting your files and emptying the recycle bin. 

This guide will help you make sure all of your personal data is wiped from the machine so you can be confident it’s all gone before you give it away or recycle it. 

First things first: Back up your computer

Before you do anything, make sure your data is backed up. You want to be able to load it all on to a new computer, or at least keep it in an archive, so you can access it after you dispose of your old machine. The best plan for backing anything up is the 3-2-1 backup strategy where you keep three copies of your data on two types of media with one copy off-site. Your first copy is the one on your computer. Your second copy can be kept on an external hard drive or other external media. And, your third copy should be kept in an off-site location like the cloud. If you’re not backing up an off-site copy, now is a great time to get started.

You can easily create a backup using Windows Backup on Windows 7, 8, 8.1, 10, and 11. If you save that to an external hard drive, you can then move your files to a new computer or just keep it as a local backup. Once you’re backed up, you’re ready to wipe your PC’s internal hard drive.

How to completely wipe a PC

In most cases, wiping a PC involves simply reformatting the disk and reinstalling Windows using the Reset function. If you are recycling, donating, or selling your PC, the Reset function makes data recovery sufficiently difficult, especially if your data is encrypted (more on that later). This process is straightforward in Windows versions 8, 8.1, 10, and 11, and works for both hard disk drives (HDDs) and solid state drives (SSDs).

How to reset Windows 10 and 11

Follow these instructions for different versions of Windows to reset your PC:

  1. Go to Settings → System (In Windows 10: Update & Security) → Recovery.
  2. Under Reset this PC, click Reset PC. (In Windows 10: Click Get Started.)
  3. Choose Remove everything. If you’re not getting rid of your PC, you can use Keep my files to give your computer a good cleaning to improve performance.
  4. You will be prompted to choose to reinstall Windows via Cloud download or Local reinstall. If you’re feeling generous and want to give your PC’s next owner a fresh version of Windows, choose Cloud download. This will use internet data. If you’re planning to recycle your PC, Local reinstall works just fine.
  5. In Additional settings, click Change settings and toggle Clean data to on. This takes longer, but it’s the most secure option.
  6. Click Reset to start the process.

How to reset Windows 8 and 8.1

  1. Go to Settings → Change PC Settings → Update and Recovery → Recovery.
  2. Under Remove everything and reinstall Windows, click Get started, then click Next.
  3. Select Fully clean the drive. This takes longer, but it’s the most secure option.
  4. Click Reset to start the process.

Secure erase using third-party tools

If the reset option doesn’t totally put your mind at ease, or if you have a PC running Windows 7 or older, you have another option—third-party tools. There are a number of good third-party tools you can use to securely erase your disk, which we’ll get into below. These are different depending on whether you have an internal HDD or an SSD.

How do I find out I have an HDD or SSD in my Windows laptop?

Most desktops and laptops sold in the last few years will have an SSD, but you can easily check to be sure:

  1. Open Settings.
  2. Type “Defragment” in the search bar.
  3. Click on Defragment and Optimize Your Drives.
  4. Check the media type of your drive.

How to securely erase your Windows drive using third-party tools

Now that you know what kind of drive you have, here are your options for wiping your Windows drive:

Securely erase an HDD

The process for erasing an HDD involves overwriting the data, and there are many utilities out there to do it yourself:

  1. DBAN: Short for Darik’s Boot and Nuke, DBAN has been around for years and is a well-known and trusted drive wipe utility for HDDs. It does multiple pass rewrites (binary ones and zeros) on the disk. You’ll need to download it to a USB drive and run it from there.
  2. Disk Wipe: Disk Wipe is another free utility that does multiple rewrites of binary data. You can choose from a number of different methods for overwriting your disk. Disk Wipe is also portable, so you don’t need to install it to use it.
  3. Eraser: Eraser is also free to use. It gives you the most control over how you erase your disk. Like Disk Wipe, you can choose from different methods that include varying numbers of rewrites, or you can define your own.

Keep in mind, any disk erase utility that does multiple rewrites is going to take quite a while to complete.

If you’re using Windows 7 or older and you’re just looking to recycle your PC, you can stop here. If you intend to sell or donate your PC, you’ll need the original installation discs (yes, that’s discs with a “c”…remember? Those round shiny things?) to reinstall a fresh version of Windows.

Don’t worry. You can still make use of those discs.

Securely erase an SSD

You have a few options for securely erasing an SSD. These third-party tools will do the trick:

  1. Parted Magic: Parted Magic is the most regularly recommended third-party erase tool for SSDs, but it does cost $11. It’s a bootable tool like some of the HDD erase tools—you have to download it to a USB drive and run it from there.
  2. ATA Secure Erase: ATA Secure Erase is a command that basically shocks your SSD. It uses a voltage spike to flush stored electrons. While this sounds damaging (and it does cause some wear), it’s perfectly safe. It doesn’t overwrite the data like other secure erase tools, so there’s actually less damage done to the SSD.

Encrypting data on a Windows PC

Even if you’re not getting rid of your computer, encrypting your data is a good idea. If your laptop falls into the wrong hands, encryption makes it that much harder for criminals to access your personal information. But, if you have an SSD, encrypting your data is even more important, both before you get rid of it and just in general. Why? The way SSDs store and retrieve data is different from HDDs.

HDDs store data at specific physical locations on the drive platter. In contrast, SSDs use electronic circuits and memory cells, which are organized into pages and blocks, to store data. Constant writing and rewriting to the same blocks can wear out an SSD over time. To mitigate this, SSDs employ a technique called “wear leveling,” which distributes data across the entire drive, preventing it from being stored in just one physical location.

When you tell an SSD to erase data, it doesn’t overwrite the existing data. Instead, it writes new data to a different block. Consequently, some of your old data may remain on the SSD until the wear leveling process eventually overwrites those cells. So, it’s smart to encrypt your data before erasing it from an SSD. This ensures that any residual data is protected. If any data is left lurking, at least no one will be able to read it without an encryption key.

Encrypting your data first isn’t necessarily a requirement, but if Windows Reset is not enough for you and you’ve come this far, we figure it’s a step you’d want to take. The process isn’t complicated, but not every Windows machine is the same. First, check to see if your device is encrypted by default:

  1. Open the Start menu.
  2. Scroll to the Windows Administrative Tools dropdown menu.
  3. Select System Information. You can also search for “system information” in the taskbar.
  4. If the Device Encryption Support value is “Meets prerequisites,” you’re good to go—encryption is enabled on your device.

If not, your next step is to check if your device has BitLocker built in:

  1. Open Settings.
  2. Type “BitLocker” in the search bar.
  3. Click Manage BitLocker.
  4. Click Turn on BitLocker and follow the prompts.

If neither of those options are available, you can use third-party software to encrypt your internal SSD. VeraCrypt and AxCrypt are both good options. Just remember to record the encryption passcode somewhere and also the operating system (OS), OS version, and the encryption tool you used so you can recover the files later on if desired.

The nuclear option

Encrypting, resetting, and/or wiping your drive with a third-party tool should be more than enough to make sure your data is protected and your laptop or desktop is clean before you donate or recycle it. But maybe you’re still feeling wary about it. In that case, you always have the option to destroy the drive yourself.

When nothing less than total destruction will do, just make sure you do it safely. The safest and most secure way to destroy an HDD, and the only way we’d recommend physically destroying an SSD, is to shred it. Check with your local electronics recycling center to see if they have a shredder you can use. (And, you absolutely want to ask if you can watch as giant metal gears chomp down on your drive. Metal.) Shredding it should be a last resort though. Drives typically last five to 10 years, and millions get shredded every year before the end of their useful life. 

If you have a megabot ready to go, you should first crush, then shred your drives.

Still have questions about how to securely erase or destroy your hard drives? Let us know in the comments. And if you’re curious about how to erase a Mac HDD or SSD, read our guide here.

FAQs

How do I wipe a PC?

In most cases, wiping a PC involves simply reformatting the disk and reinstalling Windows using the Reset function. If you are recycling, donating, or selling your PC, the Reset function makes data recovery sufficiently difficult, especially if your data is encrypted. You can also use third-party tools to securely wipe a PC drive.

How do I encrypt data on a PC drive?

First, check to see if your device is encrypted by default. You can search “system information” in the search bar. If the Device Encryption Support value is “Meets prerequisites,” you’re good to go—encryption is enabled on your device. If not, your next step is to check if your device has BitLocker built in. Type “BitLocker” in the search bar, click Manage BitLocker, then click Turn on BitLocker and follow the prompts. If neither of those options are available, you can use third-party software to encrypt your internal SSD. VeraCrypt and AxCrypt are both good options.

How do I safely dispose of an SSD or HDD myself?

The safest and most secure way to destroy an HDD, and the only way we’d recommend physically destroying an SSD, is to shred it. Check with your local electronics recycling center to see if they have a shredder you can use (or if they’ll at least let you watch as giant metal gears chomp down on your drive). Shredding it should be a last resort though. Drives typically last five to 10 years, and millions get shredded every year before the end of their useful life. 

The post Getting Rid of Your PC? Here’s How to Wipe a Windows SSD or Hard Drive appeared first on Backblaze Blog | Cloud Storage & Cloud Backup