Post Syndicated from The Atlantic original https://www.youtube.com/shorts/zaP7tce_EN0
A Conversation With Gina Raimondo
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=J52fDKpeUjY
Searcy, Arkansas Missile Silo Fire: 1965
Post Syndicated from The History Guy: History Deserves to Be Remembered original https://www.youtube.com/watch?v=azGt_Z1A8UI
Are AIs Still Struggling with CAPTCHAs?
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2026/09/are-ais-still-struggling-with-captchas.html
Anthropic’s recent security-incident document contains a bit about how CAPTCHAs are still frustrating Claude.
In the transcript, the Claude model that is so powerful that Anthropic is gatekeeping access to it appeared to slam its virtual head against the wall solving a simple image identification test. In a test where the agent was asked to identify a shape that didn’t match the others displayed, it couldn’t even decide which image to select. Instead, it repeatedly went over the same images and questioned its own conclusions.
“Actually hmm, wait,” it said in its chain-of-thought transcript, later adding “Ugh,” because we’ve decided that we need to inject human mannerisms into these machines for some reason. The whole thing took so long that the agent eventually realized that the challenge had expired and it would have to start the process again.
At one point, the model struggled to recognize that the CAPTCHA had opened in a new window and couldn’t figure out what its next steps were supposed to be. At one point, it theorized that the test might be “broken by design” and presented human-like anger in its transcript meant for a human audience: “SO WHAT THE HELL IS WRONG WITH THE ANSWERS?”
Meanwhile, I’ve read reports—none of them official—that GPT-6 Astra solved all forty-eight levels of Neal Agarwal’s “I’m Not a Robot” game.
It’s hard to know what to believe right now.
Как държавата режисира ужаса от Петрохан
Post Syndicated from Емилия Милчева original https://www.toest.bg/kak-durzhavata-rezhisira-uzhasa-ot-petrohan/
Властта умее да режисира ужаса така, че сама да остане извън кадър, когато е необходимо. Показва ни отблизо чудовище – деянията му, жертвите, най-интимните подробности от чуждите травми, и ни оставя да поискаме още от същото. Една част от хората избират да се отвратят от чудовището, друга – от институциите манипулатори, трета, най-малката, и от двете.
Така беше режисиран ужасът от Петрохан шест седмици преди президентските избори. След осем месеца разследване и неприключило досъдебно производство прокуратурата и МВР избраха да разкажат какво е извършил т.нар. лама Ивайло Калушев – мъртъв, както и останалите петима от затворената общност, обитавала планинска хижа; човекът, манипулирал възрастни и прекрачил границите с деца, поверени му за отглеждане от родителите им по неясни причини.
Заключенията са, че няма данни за външна намеса, тоест екзекуторите трябва да се търсят в самата група, и делото най-вероятно ще бъде прекратено, тъй като извършителите са мъртви.
Като главен секретар на МВР Георги Кандев също беше съобщил, че няма данни за външна намеса нито на Околчица, нито на Петрохан.
Огласената версия е, че Ивайло Калушев, застрелял 22-годишния Н.З. и 15-годишния А.М., е организирал фаталния край на групата поради страх от разкрития за действията му с деца.
Кръв, порно, политика
Това, което дават по новините, е белег за нещо отдавна случващо се под носа ни: умишления отказ на институциите да си вършат работата. Коментар на Емилия Милчева.
Гавра с правосъдието
На двучасова пресконференция криминалният психолог Росен Йорданов произнесе моралната присъда, въпреки че няма обвинение, и нареди пред публиката секс с подрастващи, окултни практики, манипулации, оръжия и шест трупа. Говореше ту като вещо лице, ту „като човек“, остро и назидателно, сякаш не представя експертно заключение, а защитава обвинителна теза пред съдебни заседатели. Само че съдебни заседатели нямаше, имаше камери и оставаше само някой да разпространи „обвинителния акт“.
Поведението на Йорданов допълнително разруши и без това оскъдното доверие в разследването и в институции като МВР и прокуратурата. Още на 10 и 15 февруари пред БНТ, преди да бъде назначен за вещо лице и преди да получи достъп до материалите, той вече беше определил Калушев като човек с „тежки нарцистични проблеми“, „професионален прелъстител и педофил“ и беше обяснил мотивите му. На 17 март същият психолог е привлечен като експерт, за да изследва безпристрастно именно личността, поведението и мотивите, за които вече публично е произнесъл присъдата си.
Затова адвокатите Ина Лулчева и Деница Тодорова, представляващи близки на загиналите, поискаха от прокуратурата да отстрани Йорданов и още две вещи лица заради пристрастност и предубеденост. Адвокат Димитър Марковски нарече пресконференцията „груба грешка“ – при 12 незавършени експертизи прокуратурата е фаворизирала една версия, преди да е приключило събирането и проверката на доказателствата. По БНР правозащитникът адвокат Михаил Екимджиев определи поведението на Йорданов като „фрийкшоу“ извън нормалните представи за професионална етика.
Самият Йорданов отказа да се оттегли. Обяви, че не е предубеден, а емоционален – заради случая. За адвокатите, поискали отвода му, каза:
Те нямат какво друго да направят.
Този отказ не е маловажен професионален спор. Ако прокуратурата запази представената версия, наказателното производство за убийствата ще бъде прекратено, защото посочените извършители са мъртви. Няма да има открит съдебен процес, в който експертизата да бъде оспорена, вещите лица да бъдат разпитани, защитата да представи други доказателства и съдът да прецени коя версия издържа. Евентуалната жалба срещу прекратяването ще бъде разгледана в закрито заседание.
Така публичният разказ на един експерт, нает от прокуратурата, може да остане единствената присъда.
Ето така държавната режисура постига целта си. На обществото е даден достатъчно ужасяващ разказ, за да не пита защо трябва да му се вярва. Но доверие в институциите, още по-малко в българската съдебна система няма – дори и да казват част от истината.
Да се разобличи прокуратурата не означава Калушев да бъде превърнат в невинна жертва на зли сили. Един критично мислещ човек няма да приеме присъда без съд, нито пък безусловна реабилитация на мъртвия. Съмненията в институция с дълга история на избирателни течове и политическа употреба не изключват тревожните факти за деца, оставени под едноличната власт и опека на възрастен мъж и откъснати от училище и семейство.
Калушев не става невинен само защото прокуратурата злоупотребява с фактите и обслужва определени интереси. Нито пък самата прокуратура става достойна за доверие поради избора на убедително чудовище.
В престрелката между основните лагери, на които се разполови общественото мнение, се изгубиха децата – жертви на възрастни, отказали да изпълнят задълженията си.
Сексуалните престъпления срещу деца. Институционална и обществена слепота
В предишната си статия Теодора Станимирова представи данни, разкриващи системното безсилие на институциите спрямо сексуалните злоупотреби с деца. В продължението на темата Теодора разговаря с експерти, за да разбере каква е реалната ангажираност на обществото и институциите – отвъд популизма.
Гаврата с децата
Задочната психологична експертиза беше „предоставена“ за публикуване в сайта „Епицентър“, чиято главна редакторка Валерия Велева не се посвени да я пусне, без да бъдат заличени имената на децата, посочени като жертви на обявилия се за лама. През март 2010 г. лидерът на ДПС Ахмед Доган ѝ написа отворено писмо, обръщайки се към нея с прозвището „Мадам В.“, и я обвини в корупция и търговия с влияние.
Днес, 16 години по-късно, политическата употреба се оказа по-важна от защитата на децата (и техните родители). Асоциацията на европейските журналисти (АЕЖ) обяви, че ще сезира Държавната агенция за закрила на детето, Комисията за защита на личните данни и ГДБОП.
Междувременно Велева напусна инициативния комитет на кандидатпрезидентската двойка Илияна Йотова – Кирил Вълчев след призиви да се оттегли. От самия инициативен комитет се разграничиха „от публичното изнасяне на лични данни, независимо от случаите, за които се отнася това“.
Оттеглянето ѝ не отговаря на главния въпрос:
Кой нарежда на прокуратурата да продължи практиката от времената на главните прокурори Иван Гешев и Борислав Сарафов за манипулации чрез течове на материали от досъдебни производства?
Има и друг съществен аспект – за ролята на контраразузнаването в аферата „Петрохан“. Според лидера на „Продължаваме промяната“ Асен Василев ДАНС е знаела какво се случва в хижа „Петрохан“ още от 2022 г. и е бездействала.
Очевидно някой в ДАНС покровителства групи, които нанасят щети на българските деца… Истинският въпрос е, когато са подавани сигнали в ДАНС през 2022 г., къде е спал ДАНС три години, какво е направил, кой в ДАНС е покровителствал това нещо, защо ДАНС не са сигнализирали прокуратурата.
И получи отговор от шефа на ДАНС Пламен Тончев:
Проверете делото, образувано в прокуратурата през януари 2025 г. по информация на ДАНС. Там има всички пунктове и точки, които са изнесени в обвинението и днес, само че тогава, ако някой беше реагирал навреме, тези хора може би щяха да бъдат живи.
В документа от януари е била спомената и педофилия. Самият Тончев, назначение на Румен Радев, оглавява ДАНС от 2021 г., с известно прекъсване, когато беше преместен като шеф на Комисията по досиетата.
Всъщност още през февруари, десетина дни след откриването на труповете, разследващият сайт bird.bg публикува секретната справка от ДАНС. Още тогава стана ясно, че прокуратурата не е свършила нищо по преписка за „извършени сексуални или блудствени действия от Ивайло Калушев, относими към Глава Втора, Раздел VIII от Наказателния кодекс“.
Резултатът от прехвърлянето на преписката между три прокуратури са тримата мъртъвци от „Петрохан“ и другите трима, един от които дете, в кемпера под връх Околчица.
А до фаталните изстрели 15-годишният А.М. е живял в затворената общност, откъснат от обичайния си семеен и училищен живот. Преди него в същата среда и под контрола на Калушев там е израснал от малък и Н.З.
Родителите може да са били манипулирани, че поверяват децата си на т.нар. лама. Това обаче не отменя отговорността им – родителството не може да бъде преотстъпено на самопровъзгласил се духовен водач заедно с правото му да контролира всекидневието, образованието и съзнанието на детето.
Частното училище „Космос“, където е бил записан А.М., също е допуснало продължителните му отсъствия да не задействат системата за закрила. А сега прокуратурата разследва нарушения при приема на ученици и издаването на документи с невярно съдържание, както и неизпълнение на задължения от служители на училището, МОН и регионалното управление.
Около тези деца е имало кръг възрастни – родители, учители, чиновници и контролни органи. И от всичко това излиза, че държавата, която не успява да забележи навреме изчезването на едно дете от обичайната му среда, все пак успява да забележи интимните подробности от живота му и дори решава да ги покаже на всички. Емил Дечев, служебен министър на вътрешните работи в кабинета „Гюров“, ясно посочи, че „големият отсъстващ е българската прокуратура“, и призова за обективно разследване на всички версии.
Шест седмици преди президентските избори случаят „Петрохан“ е превърнат в оръжие за политическо поразяване на силите, подкрепили кандидатпрезидентската двойка Андрей Гюров и Георги Кандев, също и на кмета на София Васил Терзиев. Както стана ясно по-рано, Терзиев е дарил над 125 000 евро лични средства за дейността на групата и е посещавал нееднократно хижата.
Какво (не) знаем за сексуалните злоупотреби с деца
Какво знаят институциите за сексуалните злоупотреби с деца в България и какви мерки предприемат? Теодора Станимирова се сдоби с информация от ВСС, МВР, АСП, ДАЗД и МЗ, разговаря с експерти и ни разказва какво е научила.
Паралелно с това премиерът Румен Радев също не се засрами да употреби децата.
Той избра училищния двор и първия учебен ден, за да нарече организацията „свърталище на педофилия“, а Калушев – „хладнокръвен убиец на деца и откровен педофил“. След психолога експерт Йорданов, който се похвали, че премиерът му благодарил, сега и Радев произнесе присъда, преди да е приключило разследването.
Държавата, която не опази децата от „Петрохан“, подреди други деца за фон на закъснялото си възмущение.
Какво се скри в мъглата?
Чудовището се оказа твърде удобно за властта. Колкото по-дълго гледаме него, толкова по-малко забелязваме растящите цени на горивата и газа, които внасят инфлация.
След президентските избори на 25 октомври случаят „Петрохан“ ще бъде изместен от първите сметки за отопление и от увеличените разходи за живот. Последните данни на националната статистика за август показват инфлация от 5,1% на годишна база и ускоряваща се през последния летен месец.
В мъглата се скри границата между познанство, дарение, политическа подкрепа и съучастие. Имената на политици бяха вкарани в един и същ разказ с убийства и сексуално насилие, без да са представени данни, че са знаели за тях. Така вината по асоциация свърши онова, за което доказателствата не стигат – превърна контактите с Калушев в политическо обвинение.
Не сме длъжни да избираме от какво да се отвратим. Достатъчно е да знаем, че институциите не защитиха децата, но пристигнаха навреме за камерите.
A Conversation With Colin Kaepernick
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=_-CZtcEN9r0
Maggie Haberman on whether Donald Trump may try to seek a third term
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/en7tERE6uYY
America 250: The Many Americans Who Made America
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=5b6gQZIwSEk
Andrew McCarthy shares his journey to understand male friendships
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/nCnQBr2txaM
Comic for 2026.09.18 – Ed Gein
Post Syndicated from Explosm.net original https://explosm.net/comics/ed-gein-3
New Cyanide and Happiness Comic
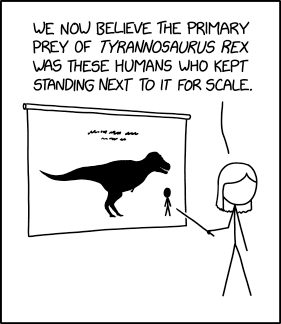
Tyrannosaurus
Post Syndicated from xkcd.com original https://xkcd.com/3300/
Inside Washington With The Atlantic’s Politics Team
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=2c85x4YGSec
A Conversation With Whitney Wolfe Herd
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=hoQ_wkclpSA
Conversations With Rob Bonta, John Formella, and David Sunday
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=CoKia8W3Yoc
Run open weight models on AWS Bedrock in AWS European Sovereign Cloud
Post Syndicated from Marta Taggart original https://aws.amazon.com/blogs/security/run-open-weight-models-on-aws-bedrock-in-aws-european-sovereign-cloud/
European organizations can run AI workloads on Amazon Web Services (AWS) while keeping data within the European Union (EU) and meeting regulatory requirements. You can now run generative AI workloads on open weight models on Amazon Bedrock in the AWS European Sovereign Cloud. We’re excited to announce the general availability of the first open weight model family, Gemma 4, on the Amazon Bedrock next-generation inference engine in the AWS European Sovereign Cloud. Gemma 4, released under the Apache 2.0 license, on Amazon Bedrock benefits from the same data residency and operational controls that define the AWS European Sovereign Cloud so you can build, iterate, and scale generative AI applications while meeting digital sovereignty requirements.
The AWS European Sovereign Cloud is an independent cloud for Europe, located entirely within the EU, designed to help customers meet their most stringent digital sovereignty requirements. It runs entirely within the EU and is independently operated with strong technical controls, sovereign assurances and legal protections. Only AWS employees who reside in the EU control day-to-day operations, including access to data centers, technical support, and customer service.
In this post, we explain how the Amazon Bedrock inference engine protects your inference data when running Gemma 4 models, how the AWS European Sovereign Cloud keeps it within the EU, and then walk through the available Gemma 4 models and your first inference request.
Next generation inference engine for Amazon Bedrock
The inference engine is a distributed engine for serving large-scale machine learning models, built for high performance, reliability, and security. You reach it through the bedrock-mantle endpoint, which supports OpenAI-compatible APIs (the Responses and Chat Completions APIs). You can bring an existing OpenAI SDK codebase to Amazon Bedrock by changing only the base URL and API key. The Responses API supports stateful conversation management, which rebuilds context without you passing conversation history with each request. Stored responses are scoped by Amazon Bedrock project, a logical boundary that represents a workload for access control, cost tracking, and usage monitoring.
The engine applies the same operational security practices you rely on across AWS. Access follows a least privilege model, where each operator has access only to the systems a specific task requires, and only for the time that privilege is needed. Any access to systems that store or process customer data or metadata is logged, monitored for anomalies, and audited. All your prompts and responses are kept private during inference.
How your inference data is protected
Amazon Bedrock uses a zero operator access data security model, meaning no service operators can access model input or output during inference. It also uses a zero data retention model, so by default it doesn’t store your inputs or outputs. For certain models, limited retention might apply for abuse detection (see the Amazon Bedrock abuse detection documentation). Your prompts and responses are encrypted in transit and, by default, are not shared with the model provider.
All inference stays within the eusc-de-east-1 AWS Region as described in the following section on data residency. Combined with the data residency and EU-based operations of the AWS European Sovereign Cloud, this gives organizations in highly regulated industries the confidence to run their most sensitive AI workloads in the cloud.
Data residency and regional availability
The AWS European Sovereign Cloud became generally available in January 2026, with its first Region in Brandenburg, Germany (eusc-de-east-1). It’s a separate, independently operated cloud, with infrastructure located entirely within the EU and no critical dependencies on non-EU personnel or infrastructure. All your content remains within the Region you select unless you choose otherwise. Beyond content, customer-created metadata including roles, permissions, resource labels, and configurations also stays within the EU. The AWS European Sovereign Cloud is operated exclusively by EU residents located in the EU. We’re also gradually transitioning the AWS European Sovereign Cloud to be operated exclusively by EU citizens located in the EU. During this transition period we will continue to work with a blended team of EU residents and EU citizens located in the EU.
All Amazon Bedrock inference requests, including Gemma 4, use in-Region inference in eusc-de-east-1, which keeps every request within the AWS European Sovereign Cloud. Global cross-Region inference, which routes requests across commercial AWS Regions worldwide, isn’t available in the AWS European Sovereign Cloud.
Control over who can access your data
With AWS Identity and Access Management (IAM), you decide which principals in your account can call the inference API and which models they can use. Fine-grained permissions let you grant only the access each workload needs, following least privilege, and we recommend short-lived credentials over long-term keys.
For auditing, every call to the endpoint is recorded in AWS CloudTrail, giving your security and compliance teams an audit trail of who invoked inference and when. You can also monitor usage with Amazon CloudWatch and set alarms on patterns that matter to you, such as unexpected spikes in request volume.
Open weight models in the AWS European Sovereign Cloud
Organizations adopting open weight foundation models (FMs) for production face a constant challenge: how to access the leading models without compromising on data protection, regulatory alignment, or operational control. Amazon Bedrock removes that challenge. It gives you leading open weight FMs through a fully managed service, with inference running entirely on infrastructure operated by AWS and the security and privacy controls you expect from Amazon Bedrock. Because the models are open weight, you can independently evaluate the model architecture and training methodology, benchmark your own workloads, and fine-tune on proprietary data when customization is required.
Gemma 4 is a family of open weight models, released under the Apache 2.0 license. It’s available in three instruction-tuned variants, so you can evaluate and choose the model that fits your workload. The following table provides guidance on which model to choose based on your use case:
|
Model |
Use case |
Specifications |
|
Gemma 4 31B |
Reasoning-heavy or coding-heavy with a single dense model |
30.7 billion parameter dense model with a 256 K token context window |
|
Gemma 4 26B-A4B |
Cost-sensitive at high throughput, with knowledge breadth requirements |
Mixture-of-experts model with 25.2 billion total parameters and 3.8 billion active per token, with a 256 K token context window |
|
Gemma 4 E2B
|
Latency-sensitive, on-device-style, or multimodal classification |
Compact model with 5.1 billion total parameters and 2.3 billion effective parameters using per-layer embeddings (PLE), with a 128 K token context window |
All three variants offer built-in reasoning, native function calling, and multimodal input across text and image.
Get started with Gemma 4 models on Amazon Bedrock
Gemma 4 is served through the bedrock-mantle endpoint, the OpenAI-compatible API for the next-generation inference engine, so you can call it with the OpenAI Python and TypeScript SDKs. Use the following steps to use the OpenAI Python SDK to send your first request to Gemma 4 31B in the AWS European Sovereign Cloud.
Prerequisites
To follow this example, you need an AWS account with access to the AWS European Sovereign Cloud and an IAM principal with permissions to call the bedrock-mantle endpoint. Create an IAM policy that grants the two actions this walkthrough uses, then attach it to your IAM principal. The bedrock-mantle:CreateInference action runs inference, and the bedrock-mantle:CallWithBearerToken action authenticates with an Amazon Bedrock API key. The following sample policy grants the actions this example needs. Scope the resources further for your environment as described after the policy.
Replace <account-id> and <project-id> with your own values.
Install the OpenAI SDK and the Amazon Bedrock token generator with the command pip install “openai>=2.45.0" aws-bedrock-token-generator.
Authenticate
You authenticate with an Amazon Bedrock API key. Amazon Bedrock offers two types of API keys. Short-term keys expire automatically within 12 hours and inherit the permissions of the IAM principal that generated them, which makes them the recommended choice for production. Long-term keys last until a configured expiration and are intended for development and exploration. For production, use the auto-refreshing short-term key shown in the following example, or store the key in AWS Secrets Manager.
Alternatively, you can pass a short-term API key through an environment variable. This key isn’t refreshed and expires after at most 12 hours.
Run your first inference with the Responses API
The Responses API uses a single input field and returns the generated text in output_text. Setting store to false means Amazon Bedrock doesn’t retain the request or response.
Call the Chat Completions API
You can also call the OpenAI-compatible Chat Completions endpoint directly. If you use AWS credentials instead of an API key, sign the request with AWS Signature Version 4 (SigV4), as in the following example.
Clean up
This walkthrough creates no persistent resources, so there’s nothing to delete. The short-term API keys used here expire automatically within 12 hours.
Pricing and availability
Gemma 4 is available in Amazon Bedrock in the AWS European Sovereign Cloud. You pay per token with no upfront commitment, and usage counts toward your existing AWS commitments. For current pricing, see Amazon Bedrock pricing. For model and Regional availability, see Regional availability by models.
Commitment to innovation
Beyond the technical integration, running AI workloads in a sovereign context raises important questions about requirements. As you plan AI workloads for a sovereign context, evaluate them against your organization’s requirements for data residency, model governance, and operational control. The AWS European Sovereign Cloud is designed to help you meet these requirements in the EU.
AWS is committed to making AWS the best place for European organizations to innovate with AI, without compromise. To learn more about AWS European Sovereign Cloud visit aws.eu.
If you have feedback about this post, submit comments in the Comments section below.
Padma Lakshmi Recommends Five Spices to Keep in Your Kitchen
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/deb2PNXYj5o
A Conversation With Rahm Emanuel
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=LG6_Rtil_mo
New low-cost burstable Amazon EC2 T8i instances are generally available
Post Syndicated from Channy Yun (윤석찬) original https://aws.amazon.com/blogs/aws/new-low-cost-burstable-amazon-ec2-t8i-instances-are-generally-available/
Today, we’re announcing the general availability of new low-cost burstable Amazon EC2 T8i instances powered by custom sixth generation Intel Xeon Scalable Processors (Granite Rapids), available only on AWS. T8i instances are among the lowest-cost EC2 instances and deliver up to 30% better price performance over previous generation T3 instances. These instances are designed to run a variety of low-to-moderate CPU utilization workloads such as freemium services, training and demo environments, staging and development, data processing, microservices, low-traffic websites, and login gateways.
T8i instances
Thousands and thousands of customers run various lightweight workloads on T3 instances that require small, cost-effective compute configurations. These include microservices architectures, low-traffic websites, development and testing environments, small databases, data processing jobs, and short-duration compute tasks. Many of these customers like T family’s burstable performance model, which provides a baseline level of CPU performance with the ability to burst above the baseline when needed using CPU credits.
As customers modernize their infrastructure, migrate from on-premises environments, adopt event-driven and microservices architectures, and experiment with AI inference workloads, they have asked for newer generation cost-optimized small instances, better price performance to reduce their total cost of ownership, and a seamless migration path that leverages their existing knowledge and tooling.
T8i instances address each of these requests:
- Up to 30% better price performance. Powered by the AWS Nitro System and custom sixth generation Intel Xeon Scalable Processors (Granite Rapids), T8i instances enable customers to lower their total cost of ownership with up to 30% better price performance.
- Up to 70% higher compute performance. T8i instances deliver up to 70% higher compute performance, up to 1.25x higher network bandwidth, and up to 2.4x higher EBS bandwidth compared to T3 instances.
- Seamless upgrade from T3. For existing T3 customers, upgrading to T8i is straightforward. The instances offer the same CPU credit system and the same familiar lightweight compute options customers already know. Customers simply select T8i instead of T3 and immediately benefit from improved price performance.
- Cost-effective entry point for new customers. For customers new to AWS or migrating from on-premises, T8i instances provide one of the most cost-effective entry points to run workloads that need low-to-moderate CPU utilization or for running short-duration compute tasks such as batch processing, event-driven functions, or CI/CD pipelines.
Instance specifications
T8i instances offer four sizes, each with two vCPU offered as a single core. The following table summarizes the specifications.
| Instance size | vCPUs | Memory (GiB) | Baseline Performance /vCPU (%) | CPU credits earned / hour | Network burst bandwidth (Gbps) |
| t8i.nano | 2 | 0.25 | 5 | 3 | Up to 6.25 |
| t8i.micro | 2 | 0.5 | 10 | 6 | Up to 6.25 |
| t8i.small | 2 | 1 | 20 | 12 | Up to 6.25 |
| t8i.medium | 2 | 2 | 20 | 12 | Up to 6.25 |
Like T3, T8i instances offer unique vCPU-to-memory ratios such as 1:0.25, 1:0.5, and 1:1 that are not offered by other EC2 instances. Like T3, T8i instances utilize the CPU credit system along with the Standard and Unlimited credit configuration modes. Unlimited mode is the default on T8i.
For workloads that need larger instance sizes above T8i offerings (nano, micro, small, and medium), I recommend M8i Flex instances that offer up to 30% better price performance than equivalent previous generation T3 instances along with the flexibility to scale up to 16xlarge.
Now available
Amazon EC2 T8i instances are available today in the following AWS Regions: US East (N. Virginia, Ohio), US West (Oregon, N. California), Asia Pacific (Hyderabad, Malaysia, Mumbai, Seoul, Singapore, Sydney, Tokyo), Canada (Central), and Europe (Frankfurt, Ireland, London, Paris). For Regional availability and upcoming Region expansion, search the instance type in the CloudFormation resources tab of AWS Capabilities by Region.
You can purchase T8i instances via On-Demand instances, and Spot instances with Savings Plan option coming soon. T8i instances support shared tenancy only and do not support Dedicated tenancy or Dedicated Hosts. t8i.micro and t8i.small instances are also available under the AWS Free Tier. To learn more, visit the Amazon EC2 Pricing page.
Try T8i instances in the Amazon EC2 console and send feedback to AWS re:Post for EC2 or through your usual AWS Support contacts.
— Channy
Pete Buttigieg Declares That We Need to “Get a Better Congress”
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/vzP0yUCND3c
A Conversation With Malcolm Gladwell
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=3vfKZF4kw_A