Navigating AWS Migration: Achieving Clarity and Confidence

Post Syndicated from Jack Clavette original https://blog.rapid7.com/2025/06/05/navigating-aws-migration-achieving-clarity-and-confidence/

Navigating AWS Migration: Achieving Clarity and Confidence

Migrating workloads to Amazon Web Services (AWS) represents a significant strategic opportunity, enabling greater agility, scalability, and potential for innovation. But undertaking this transition without a comprehensive strategy for visibility and security can introduce unforeseen risks, operational delays, and challenges in managing the new cloud environment effectively. A critical aspect often overlooked is the discovery and protection of sensitive data as it moves to and resides within the cloud, demanding specific attention.

Addressing security proactively is not merely a technical requirement: it functions as a crucial enabler, allowing organizations to fully realize the strategic benefits of the cloud without being hindered by security roadblocks or compliance failures.

Furthermore, bringing sensitive data protection into focus early connects the technical migration process directly to significant business risks, such as regulatory non-compliance and the potential impact of data breaches, underscoring the importance of robust security solutions for confidently realizing cloud benefits.

Integrating security across the migration lifecycle

A successful and secure migration is not achieved by treating security as an afterthought. Security considerations must be integrated throughout the entire migration lifecycle – from the initial assessment of the current environment, through mobilizing resources and establishing the cloud foundation, to the final migration and modernization phases.

Cloud migration typically involves distinct stages:

  1. Assess: Evaluating the current state, identifying assets, and understanding existing risks.
  2. Mobilize: Preparing resources and establishing a secure cloud foundation or landing zone in AWS.
  3. Migrate and modernize: Transferring workloads and potentially optimizing them for the cloud environment.

Addressing security continuously across these stages helps prevent costly delays and rework often associated with late-stage security implementations. Effective tooling and methodology are essential here.

Rapid7’s security platform is designed to support organizations through this journey, providing the necessary visibility, risk context, and security controls for a smoother transition to AWS. The platform unifies critical capabilities, aiming to provide a 360° view of the attack surface and streamlining security operations across hybrid environments.

Improving migration efficiency through unified security

Efficiency is paramount across migration phases to maintain project velocity without compromising security. Managing multiple disparate tools can impede progress and obscure visibility. Rapid7 helps streamline critical activities by unifying essential capabilities within its Command Platform:

  • Surface Command: Provides comprehensive asset discovery and attack surface management.
  • Exposure Command: Delivers vulnerability risk management, cloud security posture management, and workload protection.
  • Insight Connect: Enables security orchestration, automation, and response (SOAR).

This integrated approach offers advantages beyond simplified tool management, potentially leading to richer context through data correlation and more effective prioritization.

During assessment

Comprehensive planning requires a complete asset inventory. Surface Command accelerates the initial assessment phase through rapid, comprehensive asset discovery across internal and external inventories, including cloud environments like AWS. This helps to eliminate blind spots and identify all assets, including potentially unsecured systems, before they are considered for migration.

Subsequently, Exposure Command builds upon this asset foundation, adding vulnerability data (often leveraging capabilities from solutions like InsightVM) and risk scoring to identify critical weaknesses in on-premises systems slated for migration. It enables teams to focus remediation efforts effectively by prioritizing vulnerabilities based on threat-aware risk context before these systems move to the cloud.

During mobilize and migrate and modernize:

In these intensive phases, Exposure Command ensures the AWS landing zone and core services are configured securely according to organizational policies and industry best practices (e.g., CIS Benchmarks) through its Cloud Security Posture Management (CSPM) capabilities, while providing ongoing monitoring for misconfigurations. It also plays a critical role in managing cloud permissions by analyzing identities and access rights to help enforce least-privilege access models.

As workloads are deployed, it offers Cloud Workload Protection (CWP) and vulnerability management tailored for cloud assets, including container security. Concurrently, Insight Connect reduces the manual workload associated with security tasks. As a SOAR solution, it utilizes numerous plugins to automate repetitive processes like configuration validation, vulnerability enrichment, or initiating remediation workflows. This automation frees up valuable security and IT resources, helping maintain project velocity.

Enhancing risk management: Before, during, and after migration

Migrating to the cloud should not involve transferring existing on-premises security risks or inadvertently creating new ones in the AWS environment. Proactive risk management, integrated throughout the migration lifecycle, is essential.

  • Before migration: Surface Command’s ability to discover known and unknown assets provides a foundational inventory, helping prevent the migration of forgotten or unsecured systems. Concurrently, Exposure Command’s vulnerability management capabilities allow organizations to identify and address critical weaknesses in on-premises systems targeted for migration, leveraging threat-aware risk scoring to prioritize remediation efforts before these systems enter the cloud.
  • During migration (mobilize and migrate phases): As the AWS environment is established and workloads deployed, Exposure Command’s CSPM functions ensure secure configuration and detect drift. Its capabilities aid in managing cloud permissions and enforcing least privilege. Critically, Exposure Command integrates sensitive data discovery capabilities, leveraging technologies like InsightCloudSec or ingesting findings from services such as Amazon Macie. This provides visibility into the location of sensitive data within AWS. This data-centric context is incorporated into Exposure Command’s risk analysis, including attack path analysis, allowing teams to prioritize threats based on the potential business impact of compromised sensitive information.
  • During and after migration (modernization and ongoing operations): In modern cloud environments utilizing CI/CD pipelines, Exposure Command supports a proactive DevSecOps approach. By integrating security checks directly into the development lifecycle—scanning container images and validating Infrastructure-as-Code (IaC) templates—organizations can identify and fix security flaws before deployment to AWS. This “shift-left” strategy, facilitated by integrations with CI/CD platforms, significantly reduces the risk of introducing vulnerabilities into the production AWS environment and embeds security into cloud operations.

Building confidence through visibility and control

Achieving efficiency and robust risk management culminates in greater organizational confidence throughout the migration process and into ongoing cloud operations. Access to accurate, comprehensive data on assets (via Surface Command) and their associated vulnerabilities and risks (via Exposure Command) allows for more informed, data-driven migration planning.

This comprehensive approach enables organizations to:

  • Move beyond simple lift-and-shift approaches, using security posture data to strategically decide which workloads to migrate, identify necessary pre-migration remediation, and design secure target architectures in AWS.
  • Validate the security posture of the foundational AWS environment with Exposure Command’s CSPM capabilities, providing assurance before large-scale workload migration commences.
  • Benefit from consolidated visibility and reporting through dashboards and features like the Executive Risk View, offering stakeholders clear insights into the security status and risk landscape. This capability translates technical findings into business-relevant risk information, fostering broader confidence.
  • Leverage integrated detection and response capabilities post-migration, often orchestrated through Insight Connect, ensuring the security team is equipped to manage potential threats effectively in the new AWS environment

This comprehensive visibility and control replace uncertainty with operational readiness.

Achieving a secure and confident AWS transition

The transition to AWS offers substantial benefits in terms of agility, scalability, and innovation. However, realizing these benefits securely requires navigating the inherent complexities of migration and cloud operations.

Rapid7’s integrated solutions – Surface Command for foundational visibility, Exposure Command for comprehensive risk management (including vulnerability management, cloud security posture, workload protection, sensitive data context, and DevSecOps integration), and Insight Connect for automation and response – provide the unified capabilities needed to manage this journey efficiently and securely.

By delivering clarity and control across the entire migration lifecycle and into ongoing operations, the platform helps organizations manage the complexity of cloud security, enabling them to migrate to and operate within AWS with confidence.

Gain complete visibility for your AWS migration. Start your Surface Command free trial today.

[$] Fending off unwanted file descriptors

Post Syndicated from corbet original https://lwn.net/Articles/1023085/

One of the more obscure features provided by Unix-domain sockets is the
ability to pass a file descriptor from one process to another. This
feature is often used to provide access to a specific file or network
connection to a process running in a relatively unprivileged context. But
what if the recipient doesn’t want a new file descriptor? A feature
added for the 6.16 release makes it possible to refuse that offer.

Security updates for Thursday

Post Syndicated from jake original https://lwn.net/Articles/1024158/

Security updates have been issued by Debian (chromium and mariadb-10.5), Oracle (firefox, ghostscript, git, go-toolset:ol8, golang, kernel, krb5, mingw-freetype and spice-client-win, nodejs:20, nodejs:22, perl-CPAN, python36:3.6, rsync, varnish, and varnish:6), Red Hat (firefox, thunderbird, and webkit2gtk3), Slackware (curl and python3), SUSE (apache-commons-beanutils, apache2-mod_security2, avahi, buildkit, ca-certificates-mozilla, cloud-regionsrv-client, cloud-regionsrv-client, python-toml, containerd, containerized-data-importer, cups, curl, dnsmasq, docker, elemental-operator, elemental-toolkit, expat, firefox, freetype2, gdk-pixbuf, git, glib2, glibc, gnuplot, gnutls, gpg2, gstreamer, gstreamer-plugins-base, gtk3, haproxy, helm, java-17-openjdk, java-1_8_0-openjdk, keepalived, kernel, kernel-firmware, krb5, kubevirt, less, libarchive, libcryptopp, libdb-4_8, libndp, libpcap, libsoup, libtasn1, libvirt, libX11, libxml2, libxslt, Mesa, mozilla-nss, nghttp2, nvidia-open-driver-G06-signed, opensc, openssh, openssl-3, openssl-3, libpulp, ulp-macros, orc, pam, pam_pkcs11, pam_u2f, patch, pcp, pcr-oracle, shim, perl-Crypt-OpenSSL-RSA, podman, postgresql16, procps, protobuf, python-dnspython, python-Jinja2, python-requests, python-setuptools, python-tornado6, python-urllib3, python311, python311, python-rpm-macros, qemu, rsync, runc, rust-keylime, selinux-policy, sevctl, skopeo, sssd, SUSE Manager Client Tools, systemd, thunderbird, tiff, tpm2.0-tools, tpm2-0-tss, u-boot, ucode-intel, unbound, util-linux, vim, wget, and wpa_supplicant), and Ubuntu (linux-nvidia, python-django, twitter-bootstrap3, twitter-bootstrap4, and wireshark).

How Twitter could (somewhat) fix their encrypted DMs

Post Syndicated from Matthew Garrett original https://mjg59.dreamwidth.org/71933.html

As I wrote in my last post, Twitter’s new encrypted DM infrastructure is pretty awful. But the amount of work required to make it somewhat better isn’t large.

When Juicebox is used with HSMs, it supports encrypting the communication between the client and the backend. This is handled by generating a unique keypair for each HSM. The public key is provided to the client, while the private key remains within the HSM. Even if you can see the traffic sent to the HSM, it’s encrypted using the Noise protocol and so the user’s encrypted secret data can’t be retrieved.

But this is only useful if you know that the public key corresponds to a private key in the HSM! Right now there’s no way to know this, but there’s worse – the client doesn’t have the public key built into it, it’s supplied as a response to an API request made to Twitter’s servers. Even if the current keys are associated with the HSMs, Twitter could swap them out with ones that aren’t, terminate the encrypted connection at their endpoint, and then fake your query to the HSM and get the encrypted data that way. Worse, this could be done for specific targeted users, without any indication to the user that this has happened, making it almost impossible to detect in general.

This is at least partially fixable. Twitter could prove to a third party that their Juicebox keys were generated in an HSM, and the key material could be moved into clients. This makes attacking individual users more difficult (the backdoor code would need to be shipped in the public client), but can’t easily help with the website version[1] even if a framework exists to analyse the clients and verify that the correct public keys are in use.

It’s still worse than Signal. Use Signal.

[1] Since they could still just serve backdoored Javascript to specific users. This is, unfortunately, kind of an inherent problem when it comes to web-based clients – we don’t have good frameworks to detect whether the site itself is malicious.

comment count unavailable comments

Twitter’s new encrypted DMs aren’t better than the old ones

Post Syndicated from Matthew Garrett original https://mjg59.dreamwidth.org/71646.html

When Twitter[1] launched encrypted DMs a couple of years ago, it was the worst kind of end-to-end encrypted – technically e2ee, but in a way that made it relatively easy for Twitter to inject new encryption keys and get everyone’s messages anyway. It was also lacking a whole bunch of features such as “sending pictures”, so the entire thing was largely a waste of time. But a couple of days ago, Elon announced the arrival of “XChat”, a new encrypted message platform built on Rust with (Bitcoin style) encryption, whole new architecture. Maybe this time they’ve got it right?

tl;dr – no. Use Signal. Twitter can probably obtain your private keys, and admit that they can MITM you and have full access to your metadata.

The new approach is pretty similar to the old one in that it’s based on pretty straightforward and well tested cryptographic primitives, but merely using good cryptography doesn’t mean you end up with a good solution. This time they’ve pivoted away from using the underlying cryptographic primitives directly and into higher level abstractions, which is probably a good thing. They’re using Libsodium’s boxes for message encryption, which is, well, fine? It doesn’t offer forward secrecy (if someone’s private key is leaked then all existing messages can be decrypted) so it’s a long way from the state of the art for a messaging client (Signal’s had forward secrecy for over a decade!), but it’s not inherently broken or anything. It is, however, written in C, not Rust[2].

That’s about the extent of the good news. Twitter’s old implementation involved clients generating keypairs and pushing the public key to Twitter. Each client (a physical device or a browser instance) had its own private key, and messages were simply encrypted to every public key associated with an account. This meant that new devices couldn’t decrypt old messages, and also meant there was a maximum number of supported devices and terrible scaling issues and it was pretty bad. The new approach generates a keypair and then stores the private key using the Juicebox protocol. Other devices can then retrieve the private key.

Doesn’t this mean Twitter has the private key? Well, no. There’s a PIN involved, and the PIN is used to generate an encryption key. The stored copy of the private key is encrypted with that key, so if you don’t know the PIN you can’t decrypt the key. So we brute force the PIN, right? Juicebox actually protects against that – before the backend will hand over the encrypted key, you have to prove knowledge of the PIN to it (this is done in a clever way that doesn’t directly reveal the PIN to the backend). If you ask for the key too many times while providing the wrong PIN, access is locked down.

But this is true only if the Juicebox backend is trustworthy. If the backend is controlled by someone untrustworthy[3] then they’re going to be able to obtain the encrypted key material (even if it’s in an HSM, they can simply watch what comes out of the HSM when the user authenticates). And now all they need is the PIN. Turning the PIN into an encryption key is done using the Argon2id key derivation function, using 32 iterations and a memory cost of 16MB (the Juicebox white paper says 16KB, but (a) that’s laughably small and (b) the code says 16 * 1024 in an argument that takes kilobytes), which makes it computationally and moderately memory expensive to generate the encryption key used to decrypt the private key. How expensive? Well, on my (not very fast) laptop, that takes less than 0.2 seconds. How many attempts to I need to crack the PIN? Twitter’s chosen to fix that to 4 digits, so a maximum of 10,000. You aren’t going to need many machines running in parallel to bring this down to a very small amount of time, at which point private keys can, to a first approximation, be extracted at will.

Juicebox attempts to defend against this by supporting sharding your key over multiple backends, and only requiring a subset of those to recover the original. I can’t find any evidence that Twitter’s does seem to be making use of this, but all the backends used are under x.com so are presumably under Twitter’s direct control. Trusting the keystore without needing to trust whoever’s hosting it requires a trustworthy communications mechanism between the client and the keystore. If the device you’re talking to can prove that it’s an HSM that implements the attempt limiting protocol and has no other mechanism to export the data, this can be made to work. Signal makes use of something along these lines using Intel SGX for contact list and settings storage and recovery, and Google and Apple also have documentation about how they handle this in ways that make it difficult for them to obtain backed up key material. Twitter has no documentation of this, and as far as I can tell does nothing to prove that the backend is in any way trustworthy.

On the plus side, Juicebox is written in Rust, so Elon’s not 100% wrong. Just mostly wrong.

But ok, at least you’ve got viable end-to-end encryption even if someone can put in some (not all that much, really) effort to obtain your private key and render it all pointless? Actually no, since you’re still relying on the Twitter server to give you the public key of the other party and there’s no out of band mechanism to do that or verify the authenticity of that public key at present. Twitter can simply give you a public key where they control the private key, decrypt the message, and then reencrypt it with the intended recipient’s key and pass it on. The support page makes it clear that this is a known shortcoming and that it’ll be fixed at some point, but they said that about the original encrypted DM support and it never was, so that’s probably dependent on whether Elon gets distracted by something else again. And the server knows who and when you’re messaging even if they haven’t bothered to break your private key, so there’s a lot of metadata leakage.

Signal doesn’t have these shortcomings. Use Signal.

[1] I’ll respect their name change once Elon respects his daughter

[2] There are implementations written in Rust, but Twitter’s using the C one with these JNI bindings

[3] Or someone nominally trustworthy but who’s been compelled to act against your interests – even if Elon were absolutely committed to protecting all his users, his overarching goals for Twitter require him to have legal presence in multiple jurisdictions that are not necessarily above placing employees in physical danger if there’s a perception that they could obtain someone’s encryption keys

comment count unavailable comments

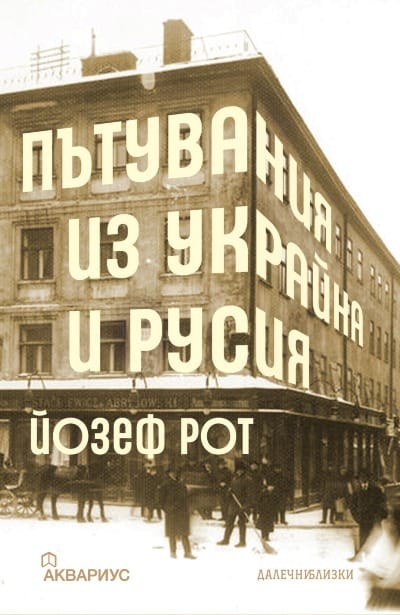
На второ четене: „Пътувания из Украйна и Русия“

Post Syndicated from Стефан Иванов original https://www.toest.bg/na-vtoro-chetene-putuvaniya-iz-ukraina-i-rusia/

„Пътувания из Украйна и Русия“ от Йозеф Рот

На второ четене: „Пътувания из Украйна и Русия“

превод от немски Ана Димова, София: изд. „Аквариус“, 2020

Йозеф Рот, този вещ пророк на разпада, скита из Украйна и Русия между империи и идеи, а текстът му се колебае между вестникарска дописка и увод за тогавашния край на света. Вгледан в следите от наскоро отминалите катастрофи, той пише с журналистическата прецизност и меланхолията на изгубения и нежелан човек.

Двайсетте години на миналия век са момент на имперски махмурлук – Австро-Унгария я няма, Русия е преминала през революция и гражданска война, Полша е отново на картата (в леко наперено настроение).

И в тези разпокъсани територии Рот вижда не картография, а психография. Той измерва не граници, а чувства, не документи, а самота.

В Украйна вижда народ без държава, във Варшава – държава, която не иска народите си, а Русия е експеримент, който изглежда едновременно свещен, страшен и наивен.

Рот започва с великолепна сатира за модата по Украйна в Берлин. Една украиномания владее Германия – оперетна, кичозна, вариететна. Украинци, които играят с нож в зъбите като индианци, западняци, които имитират казашки пантомими. Тази мимикрия на културната идентичност през карнавал има неочакван паралел с днешните инфлуенсърски иронични етнокостюми – култури, сведени до филтри и постове, докато действителната история бива заглушена. Да, забавлявайте се с чуждото, когато собственият ви свят се разпада. Модата остава на мода.

Рот преминава в гневна емпатия и описва украинците като народ, който не е можел да бъде себе си, а е бил подчиняван от големите сили. Той вижда националната идентичност не като даденост, а като реакция към бедност, към несправедливост, към това, че интелектуалецът е русофил, докато селянинът е просто гладен. И тук е гениалната му диагноза, че

националното се събужда, когато те обявят за никой.

Докато Капушчински разказва за Африка или Иран с постколониална чувствителност и лаконичност, Рот го прави за Източна Европа с пищен, мъгляв, почти мистичен език, пълен с влага, дим, руини и вина. Все едно Капушчински с душата на Томас Бернхард.

В пътеписа за Лемберг (Лвов) Рот улавя многоезичието и мързела, крехкото съжителство на култури и сакралната обърканост на Източна Европа. Пъстрота, която не крещи, град на заличени граници, където офицерът носи сладко, а евреите се разхождат в краката на статуя на Адам Мицкевич. Днес, когато Лвов е фронтова зона на културната и физическата война, тази картина звучи като недостижим спомен за нормалност, където всеки говори езика си, но живее в града на другите.

Есето за погребението на един инвалид е трагикомичен апокалипсис. Тук Рот е безмилостен и описва военните ветерани като ходещи развалини, нация от осакатени. Не можем да не мислим за съвременните образи на хора, загубили всичко. Политиката обещава величие, а резултатът е конвой от куцащи, слепи, обезумели. И да, това шествие е вечен парад на имперския провал.

Рот е бароков модернист, не се страхува от дълги описания, епитети, повторения. Той е ироничен, но не жесток. Може да се подиграе на фалшивите диадеми на украинските балерини, но никога – на босите селяни със сламени шапки. Неговият стил създава камерен театър на историята, в който реквизитът (киевска песен, петербургска мъгла и ленинградски студ) се превръща в дълбок символ на уязвимостта.

Украйна през 20-те години на ХХ век е „безгласна буква“, а през 20-те на сегашния се превърна в глас, който крещи през световния екран. Днес украинската идентичност не е предмет на берлински пантомими, а борба за съществуване, иронично също толкова непозната на Запада, който не знае разликата между Киев днес и Киев преди.

Ленинград на Рот е град, роден от волята на царя и потопен в мъглата на неразрушимото, с архитектура, която „не се руши, а се разтваря“. Звучи ли познато? Днес Кремъл не се пръска, но разтваря реалността около себе си в дим. С пропаганда, със страх и с минало, което вампирясва в саркофага си и извън него. Какво остава същото? Сляпото преклонение пред бруталната държава за сметка на живите хора. Унижението, прието с гордост.

В тази мрежа от истории и привидни независимости България е сред публиката в салона на Историята. В партера. Клати крака, аплодира или освирква поредната премиера – украинска, руска, европейска. Междувременно държи плакати с надписи от Рот:

Не ни е нужен влак, ако не искаме да стигнем там, където отива той.

Това не е пътепис, а диагноза. Не е нито литература на ужаса, нито туристически дневник, а нещо между психоанализа на нациите и политическа поезия. Рот е съвест с очила и тефтер, която вижда повече, отколкото иска, но пише така, че да ни накара да видим и ние.
Той гледа Украйна и Русия като човек, който е загубил своята родина и затова разбира по-добре тези, на които тепърва ще им я отнемат.

На второ четене: „Пътувания из Украйна и Русия“

Тази книга не крещи: „Учете за Украйна!“ Тя показва хора, в чиито думи и действия има повече свобода, отколкото в тези на дипломатите. Има човещина, има я и липсата ѝ. Селяните пеят, защото друго не им е останало. Политиците пренареждат света така, че хората изчезват от него.

Украйна продължава да бъде гледана през чужди очи и днес – от западните медии, от руската пропаганда, от българските форуми. Възприемаме я не като държава, а като сюжет. Нейната трагедия е, че най-сетне влиза в историята като субект, но с цената на кръв, трагедия и милиони прокудени. Рот го е видял в зародиш. Днешният свят го живее като епилог. Не се знае какво ще последва.

Рот показва как животът в руските покрайнини е абсурден, унизителен и нечовешки, но се понася с шеговита капитулация. Бюрократична и човешка разруха, мобилизирани мъже без ботуши, замръзнали в Сибир влакове с трупове, живот, който се движи в ритъма на патериците по паважа. Империя, която се гърчи между златната фасада, петната от кръв и дървениците. И не се знае какво ще последва.

Ако някой се чувства изгубен в днешния свят, добре дошъл е в изгубения свят на Рот. Той е пъстър, хаотичен, политически объркан, със странни конфликти и бруталност и с още по-странни национализми. Някой разпознава ли го? Да, това е нашият свят, със стари дрехи и различни имена. И той е описан от човек, който вижда как историята минава през хората като влак и не спира за никого.


Активните дарители на „Тоест“ получават постоянна отстъпка в размер нa 20% от коричната цена на всички заглавия от каталога на издателство „Аквариус“, както и на няколко други български издателства в рамките на партньорската програма Читателски клуб „Тоест“. За повече информация прочетете на toest.bg/club.

Никой от нас не чете единствено най-новите книги. Тогава защо само за тях се пише? „На второ четене“ е рубрика, в която отваряме списъците с книги, публикувани преди поне година, четем ги и препоръчваме любимите си от тях. Рубриката е част от партньорската програма Читателски клуб „Тоест“. Изборът на заглавия обаче е единствено на авторите – Стефан Иванов и Антония Апостолова, които биха ви препоръчали тези книги и ако имаше как веднъж на две седмици да се разходите с тях в книжарницата.

[$] LWN.net Weekly Edition for June 5, 2025

Post Syndicated from corbet original https://lwn.net/Articles/1022979/

Inside this week’s LWN.net Weekly Edition:

  • Front: OpenH264 in Fedora; Wallabag; Safety certification; 6.16 Merge window; Bounce buffering; Hardening repository problems; Device-initiated I/O; Faster networking; OSPM 2025; Free software in science.
  • Briefs: Kea vulnerabilities; Alpine Linux 3.22.0; Fedora strategy; Quotes; …
  • Announcements: Newsletters, conferences, security updates, patches, and more.

[$] Device-initiated I/O

Post Syndicated from jake original https://lwn.net/Articles/1022718/

Peer-to-peer DMA (P2PDMA) has been part of
the kernel since the 4.20 release in 2018;
it provides a framework that allows devices to transfer data between themselves
directly, without using system RAM for the transfer. At the 2025 Linux
Storage, Filesystem, Memory Management, and BPF Summit (LSFMM+BPF), Stephen
Bates led a combined storage, filesystems, and memory-management session on
device-initiated I/O, which is perhaps what P2PDMA is evolving toward. Two
years ago, he led a session on P2PDMA at the
summit; this year’s session was a brief update on P2PDMA with a look
at where it may be heading.

Introducing our newest 2025 AWS Heroes cohort

Post Syndicated from Taylor Jacobsen original https://aws.amazon.com/blogs/aws/introducing-our-newest-2025-aws-heroes-cohort/

The AWS community is a vibrant network of innovators, problem-solvers, and thought leaders who drive cloud technology forward. Today, we’re excited to shine a spotlight on three exceptional individuals who embody the spirit of innovation, knowledge-sharing, and community building. From architecting scalable solutions for millions of users to fostering inclusive tech groups, these professionals are making notable contributions within the AWS community. Let’s give them a warm welcome!

Christian Bonzelet – Cologne, Germany

DevTools Hero Christian Bonzelet is an AWS Solutions Architect at Bundesliga and creator of promptz.dev (a specialized prompt library for Amazon Q Developer). He brings over a decade of media and entertainment industry expertise to the AWS community. Since his first AWS project in 2013, architecting a high-scale voting system for a major German television broadcast, Christian has been passionate about AWS, serverless architecture, and AI/ML technologies. He excels at helping teams optimize their AWS implementations and develop business-aligned solutions, particularly when designing highly scalable systems serving millions of users. Known for his collaborative approach to system design and architecture, Christian actively shares his insights and experiences with the AWS community.

David Victoria – Monterrey, Mexico

Community Hero David Victoria is a senior cloud architect at Caylent. He has a Master’s in Cybersecurity and a Computer Science degree, and nine AWS certifications. With over a decade of experience delivering secure, cost-effective, and scalable solutions, David leads the AWS User Group Monterrey and helps organize the AWS Community Day México, creating spaces where thousands of builders connect and grow. His commitment to mentoring the next generation of cloud professionals across Latin America reflects his belief that “your network is your net worth.” Beyond his technical expertise, David is dedicated to fostering meaningful relationships within the AWS community, whether through public speaking, community leadership, or technical consulting.

Nora Schöner – Erlangen, Germany

DevTools Hero Nora Schöner is a senior cloud engineer with diverse industry experience who specializes in cloud architecture and DevOps. Her expertise in site reliability engineering and infrastructure as code helps teams build robust, accessible systems for both developers and stakeholders. Nora has been actively involved with AWS User Groups since 2016, co-organizing the AWS User Group Nuremberg and contributing to the AWS Community DACH Support Association. She founded She ‘n IT Nuremberg to connect women in tech and shares her unique blend of cloud technology expertise and manga art passion through her blog at wolkencode.de.

Learn More

Visit the AWS Heroes website if you’d like to learn more about the AWS Heroes program, or to connect with a Hero near you.

— Taylor

Strategy 2028 update (Fedora Community Blog)

Post Syndicated from jzb original https://lwn.net/Articles/1023837/

Outgoing Fedora Project Leader Matthew Miller has posted an update
on Fedora’s high-level plan through 2028:

[Fedora] Council members identified potential Initiatives that we
believe are important to work on next. We came up with a list of
thirteen — which is way more than we can handle at once. We previously
set a limit of four Initiatives at a time. We decided to keep to that
rule, and are planning to launch four initiatives in the next months

The initiatives are: making Fedora releases block on accessibility
issues, experimenting with a “GitOps” workflow for packaging,
migrating from Pagure to Forgejo, and “making sure Fedora
Linux is ready for people who want to work on machine learning and AI
development
“.

[$] Two sessions on faster networking

Post Syndicated from daroc original https://lwn.net/Articles/1022648/

Cong Wang and Daniel Borkmann each led session at the 2025 Linux Storage,
Filesystem, Memory Management, and BPF Summit about their respective
plans to speed up networking in the Linux kernel. Both sessions described ways
to remove unnecessary operations in the networking stack, but they focused on
different areas. Wang spoke about using BPF to speed up socket operations,
while Borkmann spoke about eliminating the overhead of networking
operations on virtual machines.

[$] The importance of free software to science

Post Syndicated from jake original https://lwn.net/Articles/1023299/

Free software plays a critical role in science, both in research and in
disseminating it. Aspects of software freedom are directly relevant to
simulation, analysis, document preparation and preservation, security,
reproducibility, and usability. Free software brings practical and specific
advantages, beyond just its ideological roots, to science, while
proprietary software comes with equally specific risks. As a practicing
scientist, I would like to help others—scientists or not—see the benefits
from free software in science.

The collective thoughts of the interwebz