From failure to success: The birth of GrabGPT, Grab’s internal ChatGPT

Post Syndicated from Grab Tech original https://engineering.grab.com/the-birth-of-grab-gpt

Introduction

In March 2023, I embarked on a mission to explore the potential of Large Language Models (LLMs) within Grab. What started off as an attempt to solve a specific problem—reducing the burden on our ML Platform team’s support channels, ended up becoming something much bigger. The creation of GrabGPT, an internal ChatGPT-like tool that has transformed how folks in Grab interact with AI. This is the story of how a failed experiment led to one of Grab’s most impactful internal tools.

The problem: Overwhelmed support channels

As part of Grab’s machine learning platform team, we were drowning in user inquiries. Slack channels were flooded with questions and our on-call engineers were spending more time answering repetitive queries than building innovative solutions. This led me to ponder on this question, “could we use LLMs to build a chatbot that understands our platform’s documentation and answers these questions automatically?”

The first attempt: A chatbot for platform support

I started by exploring open-source frameworks to build a chatbot. I stumbled upon chatbot-ui, a simple yet powerful tool that could be wired up with LLMs. My idea was to feed the chatbot our platform’s Q\&A documentation (over 20,000 words) and let it handle user queries.

But there was a catch: GPT-3.5-turbo could only handle 8,000 tokens (~2,000 words). I spent days summarising the documentation, reducing it to less than 800 words. While the chatbot worked for a handful of frequently asked questions, it was clear that this approach wasn’t scalable. I tried with embedding search and it didn’t work that well too, so I decided to give up on this idea.

The pivot: Why not build Grab’s own ChatGPT?

As I stepped back, a new thought struck me: Grab doesn’t have its own ChatGPT-like tool yet. I had the frameworks, the LLM knowledge, and most importantly—access to Grab’s model-serving platform, catwalk. Why not build an internal tool that any Grabber could use?

Over a weekend, I extended the existing frameworks, added Google login for authentication, and deployed the tool internally. I called it Grab’s ChatGPT. Little did I know, this would become one of the most widely used tools in the company.

The tool quickly became a staple for Grabbers, especially in regions where ChatGPT was inaccessible (e.g., China). The name evolved too—our PM suggested GrabGPT, and it stuck.

The Success: GrabGPT takes off

The response was overwhelming:

  • Day 1: 300 users registered.
  • Day 2: 600 new users.
  • Week 1: 900 new users
  • Month 3: Over 3000 users, with 600 daily active users
  • Today: Almost all Grabbers are using GrabGPT.
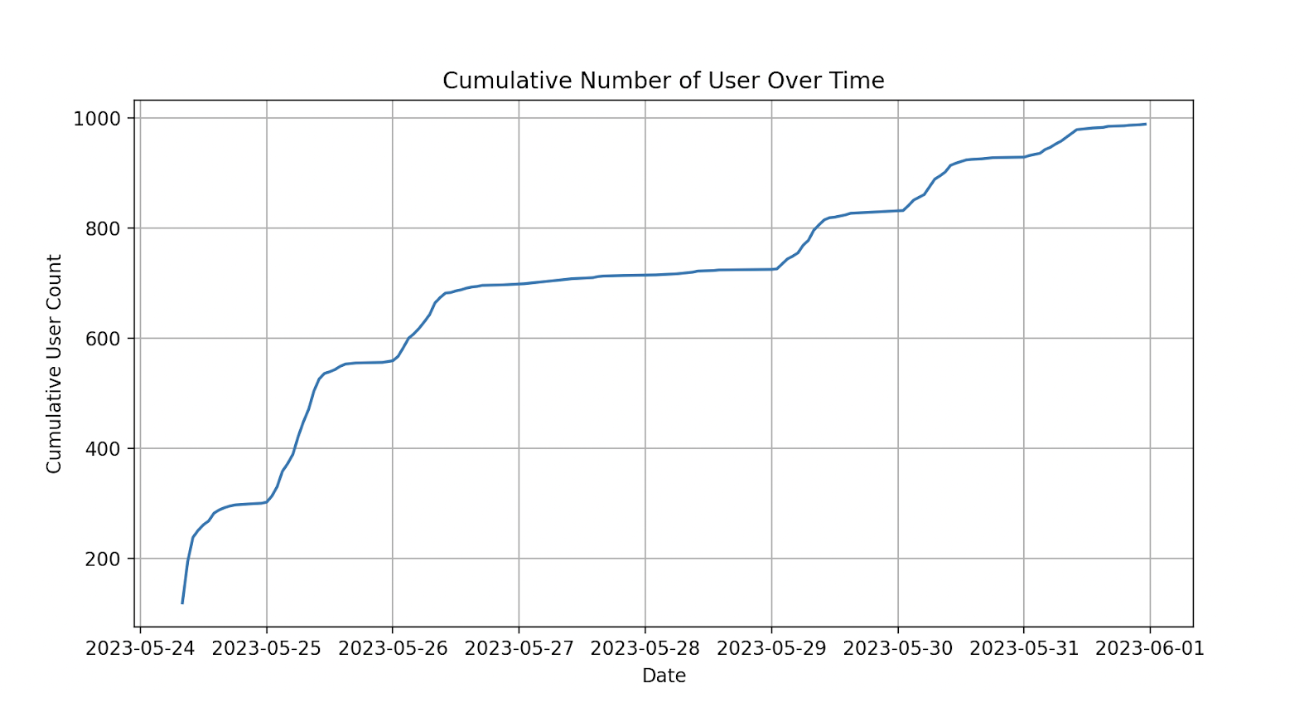
Figure 1: Number of GrabGPT users in one month

Why GrabGPT works: More than just technology

The success of GrabGPT isn’t just about the tech,it’s about timing, security, and accessibility. Here’s why it resonated so deeply within Grab:

  1. Data security: GrabGPT operates on a private route, ensuring that sensitive company data never leaves our infrastructure.
  2. Global accessibility: Unlike ChatGPT, which is banned in some regions, GrabGPT is accessible to all Grabbers, regardless of location.
  3. Model agnosticism: GrabGPT isn’t tied to a single LLM provider. It supports models from OpenAI, Claude, Gemini, and more.
  4. Auditability: Every interaction on GrabGPT is auditable, making it a favorite of our data security and governance teams.

The broader impact: A catalyst for LLM strategy

GrabGPT didn’t just solve an immediate problem, it sparked a broader conversation about how LLMs can be leveraged across Grab. It showed that a single engineer, provided with the right tools and timing, can create something transformative. Today, GrabGPT is more than a tool; it’s a testament to the power of experimentation and adaptability.

Lessons learned

  1. Failure is a stepping stone: My initial failure with the support chatbot which then led me to a much bigger opportunity.
  2. Timing matters: GrabGPT succeeded because it addressed a critical need at the right time.
  3. Think big, start small: What began as a weekend project became a company-wide tool.
  4. Collaboration is key: The enthusiasm and contributions from other Grabbers were instrumental in scaling GrabGPT.

Conclusion

GrabGPT is a story of resilience, innovation, and the unexpected rewards from thinking outside the box. It’s a reminder that sometimes, the best solution comes from pivoting away from what doesn’t work and embracing new possibilities. As LLMs continue to evolve, I’m excited to see how GrabGPT will grow and inspire even more innovation within Grab.

I would like to end this article by letting readers know that if you’re working on a project and feel stuck, don’t be afraid to pivot. You never know, your next failure might just be the beginning of your greatest success. And if you’re at Grab, give GrabGPT a try. It might just change the way you work!

Join us

Grab is a leading superapp in Southeast Asia, operating across the deliveries, mobility and digital financial services sectors. Serving over 800 cities in eight Southeast Asian countries, Grab enables millions of people everyday to order food or groceries, send packages, hail a ride or taxi, pay for online purchases or access services such as lending and insurance, all through a single app. Grab was founded in 2012 with the mission to drive Southeast Asia forward by creating economic empowerment for everyone. Grab strives to serve a triple bottom line – we aim to simultaneously deliver financial performance for our shareholders and have a positive social impact, which includes economic empowerment for millions of people in the region, while mitigating our environmental footprint.

Powered by technology and driven by heart, our mission is to drive Southeast Asia forward by creating economic empowerment for everyone. If this mission speaks to you, join our team today!
Седмицата (12–17 май)

Post Syndicated from Йовко Ламбрев original https://www.toest.bg/sedmitsata-12-17-may/

Седмицата (12–17 май)

Ако изобщо у някого са останали някакви съмнения, че президентът Румен Радев се вълнува от нещо различно освен от политическото си дълголетие, дори и ако цената е да пожертва бъдещото развитие на България, то тези съмнения трябва да са отпаднали напълно през последните десетина дни. Притоплянето на идеята за референдум за еврото само уточнява посоката на… самолета. Румен Радев недвусмислено възнамерява да е поредният, който се състезава на терена на националпопулизма.

Емилия Милчева споделя сходни размисли в коментара си по темата, озаглавен „Валутата на президента“. В него тя обобщава и важните детайли от втория мандат на Радев, който приключва догодина. На фона на доверието, с което той дебютира в политиката, намерението му да се възползва от страховете на хората, за да остане под някаква форма във властта, всъщност превръща самия него в страхливец.

Елена Телбис обаче не се страхува да нарича нещата с истинските им имена. Нито пък възнамерява да крие какъв ще е политическият ѝ дневен ред, ако вземе че стане президент. Не гласувайте за нея, моля ви! Не за друго, ама кой ще прави политическа сатира след това? А това ни е далеч по-нужно от някакъв си президент. Не на „Тоест“ – на всички ни!

Една от важните обществени теми напоследък е намерението на Министерството на образованието и науката, оглавявано от Красимир Вълчев, да въведе задължително преподаване на религия в училищата. По тази тема Донка Дойчева-Попова разговаря с проф. Мария Шнитер, която именно от позицията на преподаваща религия и ценности споделя виждания и идеи, които би следвало да отекнат с камбанен звън в главите на някои хора от МОН и Българската православна църква. Скептичен съм, че това ще стане, но интервюто е едно от задължителните ви четива за седмицата, месеца, изобщо.

На този фон, разбира се, възникват и други въпроси. Къде в приоритетите на сегашната власт стои обучението по т.нар. STEM дисциплини (абревиатурата се е наложила като термин и произлиза от английските наименования на думите наука, технологии, инженерство и математика), които се предполага да са все по-важни в бъдеще? Както и развиването на дигиталните умения в най-общ смисъл. Особено предизвикателство е комбинирането им с хуманитарните дисциплини, без които ще се отдалечим от представата си за мирен и справедлив свят.

Преди време в „Тоест“ разказахме за Елизабет Холмс и „Теранос“ – една от измамите на новия век, в която се обещаваше биотехнологична революция в кръвните медицински изследвания. В момента Холмс излежава ефективна 11-годишна присъда във федерален затвор в САЩ. В този контекст новината от седмицата, че нейният интимен партньор е успял да получи милиони долари финансиране за биотехнологичен стартъп, който с помощта на изкуствен интелект ще променя бъдещето на медицинските изследвания, е… наистина не знам какво е. Наивността, с която се подхлъзваме по модерно звучащите технологии, става все по-притеснителна.

Достъпната среда не се изчерпва с възможността да се придвижиш по тротоара. За дигиталната достъпност разказва материалът на Ивелина Гаджева и Константин Кирилов от „Екипът на София“. Европейският акт за достъпност влиза в сила след малко повече от месец и цели да защити правата на хората с увреждания да се възползват наравно с останалите от възможностите на интернет, електронното пазаруване и изобщо на мрежата като такава. В статията се обяснява как сайтовете, които ползваме ежедневно, може да се променят, за да са по-удобни за незрящи и за хора с други увреждания, а това всъщност ще ги направи по-удобни и за всички останали.

Всеизвестно е, че на хората с увреждания в България не им е лесно. И не само заради недостъпната градска или дигитална среда, качеството на медицинските грижи или административните пречки. За тях често недостъпна е дори личната им сексуалност. Това е и темата на материала на Светла Енчева тази седмица, озаглавен „Невидимата сексуалност на хората с увреждания в България“. Защото те не са пасивни обекти на грижа, пише тя, а личности с човешко достойнство.

Темата за човешките права продължава и Теодора Станимирова, която, взeмайки повод от стряскащите резултати от изследване на домашното насилие сред еднополови двойки, задава резонния въпрос защо се докарахме дотам те да нямат адекватна защита от закона. Сещате ли се защо? Защото обществото ни се остави да бъде насъскано срещу ЛГБТИ хората и да забрави, че те са… хора.

Статията на Надежда Цекулова в поредицата ни за женското здравеопазване също засяга темата за равноправието, защото, оказва се, макар вече да отминава първата четвърт на ХХI век, равното третиране на мъжете и жените в медицината все още е илюзия. Медицинските проучвания продължават да гравитират около мъжкото здраве. Данните, на чиято база се анализират заболявания, предписва се лечение, правят се лекарства и т.н., се събират от проучвания, в които преобладават мъже. В този ред на мисли заглавието на статията е съвсем на мястото си: „Пропаст в данните. Защо жените още не се побират в медицинската статистика?“

И преди да си пожелаем хубав уикенд, си позволявам да ви напомня, че съвременният свят, въпреки всички модерни технологии, така и не разполага с витален бизнес модел, който да върши работа на журналистиката, без да ѝ се налага да прави компромиси със свободата и независимостта си. Единственият начин да имаме свободни медии е те да могат да разчитат на подкрепата на своята публика.

Приятно четене!

Friday Squid Blogging: Pet Squid Simulation

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2025/05/friday-squid-blogging-pet-squid-simulation.html

From Hackaday.com, this is a neural network simulation of a pet squid.

Autonomous Behavior:

  • The squid moves autonomously, making decisions based on his current state (hunger, sleepiness, etc.).
  • Implements a vision cone for food detection, simulating realistic foraging behavior.
  • Neural network can make decisions and form associations.
  • Weights are analysed, tweaked and trained by Hebbian learning algorithm.
  • Experiences from short-term and long-term memory can influence decision-making.
  • Squid can create new neurons in response to his environment (Neurogenesis)

As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.

Metasploit Wrap-Up 05/16/2025

Post Syndicated from Spencer McIntyre original https://blog.rapid7.com/2025/05/16/metasploit-wrap-up-05-16-2025/

New modules for everyone

Metasploit Wrap-Up 05/16/2025

This week’s release is packed with new module content. We have RCE modules for Car Rental System 1.0, WordPress plugins SureTriggers, User Registration and Membership. We also have a persistence module for LINQPad software and an auxiliary module for POWERCOM UPSMON PRO. We have also added support for 32-bit architectures to our execute-assembly post module, which now supports injection of both 64-bit and 32-bit .NET assembly binaries.

New module content (5)

POWERCOM UPSMON PRO Path Traversal (CVE-2022-38120) and Credential Harvester (CVE-2022-38121)

Author: Michael Heinzl
Type: Auxiliary
Pull request: #20123 contributed by h4x-x0r
Path: gather/upsmon_traversal
AttackerKB reference: CVE-2022-38121

Description: This adds an auxiliary module for two vulnerabilities in POWERCOM UPSMON PRO: path traversal and credential harvesting. The first vulnerability allows users to traverse the path in URI and read arbitrary files with respect to privileges of a given user account. The second vulnerability allows access to sensitive credentials for UPSMON as they are stored in plaintext in a readable file.

Car Rental System 1.0 File Upload RCE (Authenticated)

Author: Aaryan Golatkar
Type: Exploit
Pull request: #20026 contributed by aaryan-11-x
Path: multi/http/carrental_fileupload_rce
AttackerKB reference: CVE-2024-57487

Description: This adds a module for a file upload vulnerability in Car Rental System 1.0. It requires administrator credentials to exploit.

WordPress SureTriggers Auth Bypass and RCE

Authors: Khaled Alenazi (Nxploited), Michael Mazzolini (mikemyers), and Valentin Lobstein
Type: Exploit
Pull request: #20146 contributed by Chocapikk
Path: multi/http/wp_suretriggers_auth_bypass
AttackerKB reference: CVE-2025-3102

Description: Adds a new exploit module for the WordPress SureTriggers plugin (≤ 1.0.78) that abuses CVE-2025-3102, an unauthenticated REST endpoint to create an administrative user and achieve remote code execution.

WP User Registration and Membership Unauthenticated Privilege Escalation (CVE-2025-2563)

Authors: Valentin Lobstein and wesley (wcraft)
Type: Exploit
Pull request: #20159 contributed by Chocapikk
Path: multi/http/wp_user_registration_membership_escalation
AttackerKB reference: CVE-2025-2563

Description: This adds a module for a privilege escalation vulnerability in the User Registration and Membership plugin for WordPress. It allows creating new users with administrator privileges.

LINQPad Deserialization Exploit

Authors: James Williams and msutovsky-r7 [email protected]
Type: Exploit
Pull request: #19777 contributed by msutovsky-r7
Path: windows/local/linqpad_deserialization_persistence
AttackerKB reference: CVE-2024-53326

Description: Adds a module to install persistence relying on CVE-2024-53326, a .NET deserialization vulnerability in the startup of Linqpad versions prior to 5.52.

Enhancements and features (3)

  • #20098 from smashery – Adds support for 32-bit execute-assembly, allowing injection of 64-bit or 32-bit .NET assembly.
  • #20126 from bcoles – This adds a Linux post-exploitation method to check Yama’s ptrace_scope setting. It removes a round trip required to obtain the scope value making modules that require knowing it to run slightly faster.
  • #20173 from adfoster-r7 – Updates the web crawling modules to support HTTP logging.

Bugs fixed (8)

  • #20010 from lafried – This fixes missing Powershell signature, when SSH is trying to identify the platform.
  • #20111 from cdelafuente-r7 – Fixes an issue that prevented failed exploit attempts to be registered in the database correctly.
  • #20118 from zeroSteiner – This fixes the target option for smb_to_ldap module. The option RELAY_TARGETS is now outdated, RHOSTS should be used instead.
  • #20120 from bcoles – This fixes typos across many Windows post-exploit modules and adds missing metadata.
  • #20128 from bcoles – This fixes an IP address assignment in the auxiliary/bnat/bnat_router module.
  • #20142 from L-codes – Fixes a crash when running unknown commands in msfconsole when using specific versions of Ruby and bundler.
  • #20156 from bcoles – This fix typos and rubocop violations inside the post modules.
  • #20181 from bwatters-r7 – This fixes an issue in Metasploit’s WordPress login functionality that would cause it to fail for certain target configurations.

Documentation added (1)

  • #20151 from adfoster-r7 – Updates the Wiki to include the latest available download links.

You can always find more documentation on our docsite at docs.metasploit.com.

Get it

As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:

If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro

The collective thoughts of the interwebz