Your Code42 renewal notice showed up with different news this year. New sales stopped at the end of 2025. Support ends at the end of 2026. After that, your backup archives get deleted.
So you start looking for a replacement, and the first name that comes up is CrashPlan.
Makes sense. Same lineage. Familiar interface. Probably assumes it’s the safe, low-effort choice, since it’s basically still Code42, right?
Not quite. And that assumption is worth slowing down on before it makes the decision for you.
CrashPlan and Code42 stopped being the same company in 2022
Code42 didn’t rebrand into CrashPlan. It sold it.
In 2022, Code42 spun off its backup business to Mill Point Capital, a private equity firm, and kept the name Code42 for what remained: Incydr, its insider risk and data loss prevention product. The backup product you knew went with the spinoff and became CrashPlan Group, a separate company under separate ownership with its own board, its own P&L, and its own reasons for making decisions.
Code42 itself was later acquired by Mimecast, which is why the backup add-on still bundled with Incydr is now the thing getting discontinued.
Two different companies. Two different endings. One of them just happens to still have “Code42” written all over your IT team’s institutional memory.
Why that matters more than it sounds like it should
If CrashPlan were still part of Code42, you could reasonably treat this as an internal product transition. A new plan, maybe a new UI, but the same company standing behind the decision.
It isn’t that. CrashPlan is a separate company that stands to gain from every Code42 customer who defaults to them without comparing alternatives. That’s not a knock on CrashPlan. It’s just how the incentive is built. A company selling you the “next step” isn’t the same thing as a neutral party recommending your best option.
Which is exactly why CrashPlan has built migration tooling specifically aimed at capturing displaced Code42 customers. It’s a smart move on their part. It’s also a reason to look closer, not a reason to skip the evaluation.
The 5TB cap nobody’s mentioning
Here’s something worth checking before you assume CrashPlan is a like-for-like replacement: some of its plans now cap storage at 5TB.
If you were on Code42 for straightforward, unlimited endpoint backup, that’s a meaningful change, not a rounding error. Plenty of IT teams don’t find out about a storage ceiling until they hit it, usually mid-migration, usually at the worst possible time to discover a gap.
Ask directly. Get the number in writing. Don’t assume “backup” means the same thing across two different companies just because one of them used to own the other.
“Enterprise data resilience” is not the same pitch as “backup”
CrashPlan has also been repositioning its messaging, moving from straightforward backup language toward broader “enterprise data resilience” positioning.
That’s not necessarily bad. It might be exactly what some organizations need. But it’s a different product story than the one you signed up for with Code42, and different stories tend to come with different pricing, different complexity, and different things bundled in whether you asked for them or not.
If what you actually need is dependable endpoint backup, a platform that’s busy becoming something bigger isn’t automatically the simpler choice. Sometimes it’s the more expensive one wearing a more ambitious name.
The question worth asking before you default to anything
Not just about CrashPlan. About whatever you’re evaluating next.
Who owns this company, and what are they optimizing for? What happens to my data and my pricing if this company gets acquired, repositioned, or sunset the way Code42’s backup product just was? Is this the vendor I’m choosing on the merits, or the one I’m choosing because switching again sounds exhausting?
That last one is real, and nobody should pretend it isn’t. Migration fatigue is a legitimate reason people make worse decisions than they would otherwise. It’s also exactly the moment worth a second look, not a shortcut.
What we’d suggest instead
Compare CrashPlan against your actual requirements, not against the assumption that it’s the default successor. Ask about storage limits in writing. Ask what “enterprise data resilience” costs versus what plain backup used to cost. And give yourself enough runway to compare more than one option, because a rushed decision made under a vendor’s deadline is usually the vendor’s deadline working exactly as intended.
If you want a second option in that comparison, we put together a migration guide that walks through what a Code42 replacement looks like on Backblaze specifically, including a realistic week-by-week timeline that doesn’t leave you without protected data at any point in the switch. Backblaze Computer Backup runs a lightweight native client and deploys silently through the MDM tools most IT teams already use, so the evaluation itself is quick even if the decision takes longer. It’s not the only option out there. It’s just one worth putting next to the others before you pick anything.
Migrating off Code42 and want to see how the timeline actually works? Talk to our team about what it would take to move your environment to Backblaze.
If you’re running a Mac fleet, Jamf is often where everything starts. It handles provisioning, policies, app installs——the orchestration that keeps your fleet sane. But backup is the thing that doesn’t fit. Jamf gives you control over every Mac, but it doesn’t protect the data on them. Backblaze closes that gap without changing how your team works.
Webinar: Building a Complete Mac Protection Strategy
Join Solution Engineers from Jamf and Backblaze for a practical discussion on building a complete Mac protection strategy.
The device ownership problem
Either you know who owns every device upfront (rare), or you don’t (common). Most teams end up doing some mix: devices that came pre-assigned, devices still waiting for user mapping, devices that migrated between teams. You write a script to fix it, then another to catch the next variation. Three months later, you’re not sure if every device is actually backed up or just supposed to be.
The new solution: Two ways to match devices to users. Pick the one that matches your reality.
This update solves the core friction: you don’t have to choose one deployment model anymore.
Method 1: Fixed email (for controlled environments) If you already know who owns each device at install time, for example, if you have clean HR data synced to Jamf, you can pass the user email directly during deployment. The installer uses it to set up the account automatically. No guessing, no drift.
Method 2: Dynamic user detection (for real-world environments) If you don’t have clean data upfront (e.g. when new devices arrive, get imaged, and wait for assignment) the installer waits until a user logs in. Once a user signs in, Backblaze can automatically associate the device with the appropriate user account based on the deployment configuration and identity information available on the device. This reduces the need for manual user assignment and helps prevent devices from being left unprotected.
Or mix them: some devices get email, others get dynamic detection. The system can now handle both in the same deployment.
What this means for your workflow
You push the Backblaze installer through a Jamf policy, same as any other app. Set your preferred method (fixed or dynamic) once at the group level, then let it run. Devices show up in the Backblaze console under the right user, with the right backup scope, no extra steps.
When something does need adjustment—a device moved teams, a user credential changed—you handle it the same way you’d handle any other Jamf-managed app. Script it, reconfigure it, whatever your existing process is. Backup can now follow the same deployment and management workflows your team already uses for other Jamf-managed applications.
Fewer things that can go wrong means less time managing edge cases
The friction point used to be this: you’d deploy backup, then spend the next week chasing down why a handful of devices aren’t appearing correctly. Someone’s account didn’t match. A device landed in the wrong group. Now you’re writing workarounds.
With two deployment methods that actually handle different scenarios instead of forcing everything into one model. The new deployment options reduce common onboarding issues that often require follow-up troubleshooting.Fewer edge cases means fewer scripts to maintain, fewer devices to manually fix, fewer things to check on at 3am.
It still runs the same way once it’s installed
Nothing else about Backblaze changes. It backs up user data automatically, without caps or limits. Pricing stays flat per device. Restore works the same way. This update is purely about getting it deployed cleanly—the actual backup part just keeps working.
How to start
Pick a small group of devices. Deploy through Jamf. Watch what happens for a week. You’ll see pretty quickly whether the user-matching is working and whether this fits your environment.
Organizations rarely struggle with a lack of storage options. More often, they struggle with determining which solution best fits the way their data is created, accessed, and protected: backup versus cloud storage.
That’s especially true when evaluating backup and cloud storage solutions.
The terms are often used interchangeably, but backup and cloud storage are designed to solve different problems. Understanding those differences can help you build a more effective data protection strategy—whether you’re protecting a personal laptop, a growing media archive, employee endpoints, or critical business data.
At Backblaze, Computer Backup and B2 Cloud Storage serve distinct purposes. For some customers, one solution is the clear choice. For others, the strongest approach combines both.
Before comparing features, it’s helpful to start with a few foundational questions.
The answers often reveal whether you’re primarily trying to protect a computer, store data in the cloud, or address both needs at the same time.
When the goal is protecting a computer
For many individuals and businesses, the most important data still lives on laptops, desktops, and attached external drives.
A photographer may keep active projects on a workstation. A consultant may store client files locally. A small business may rely on employee laptops as the primary location where work is created and managed.
In these situations, the primary concern isn’t cloud infrastructure. It’s protecting the device where the work happens.
That’s where Backblaze Computer Backup fits.
Computer Backup is designed to automatically protect data stored on a Mac or Windows computer, including connected external hard drives (but not NAS devices). Once installed, it runs continuously in the background, backing up files without requiring users to manually manage folders, storage allocations, or backup schedules. For organizations looking to protect NAS data, B2 Cloud Storage can serve as a backup destination through a variety of supported third-party backup and sync tools.
The value becomes clear when something goes wrong:
A laptop is stolen.
A hard drive fails.
Files are accidentally deleted.
A ransomware attack impacts local data.
A computer needs to be restored after a hardware issue.
In each case, the goal is recovery.
Computer Backup is often a good fit when:
Your most important data lives on a computer.
You want automatic, continuous protection.
You need to recover from device loss, hardware failure, or accidental deletion.
You want a solution that requires minimal administration.
Your primary concern is protecting endpoints.
For many professionals, families, and small businesses, those requirements align closely with their day-to-day reality.
When the goal is storing and managing data in the cloud
As organizations grow, data often becomes less tied to individual devices.
Files are shared across teams. Backup software protects servers and NAS devices. Applications generate and consume data continuously. Data needs to remain accessible and manageable independent of the original device, whether that’s for long-term retention, team access, application workflows, or infrastructure backups.
At that point, the challenge shifts from protecting a computer to managing data itself.
That’s where Backblaze B2 Cloud Storage comes in.
Unlike endpoint backup, cloud object storage is designed to store data independently of any single device. Data can be uploaded, accessed, managed, shared, and integrated into workflows across users, systems, and applications.
Organizations use B2 Cloud Storage for a wide range of use cases, including:
In these environments, accessibility, scalability, and integration often matter just as much as protection.
B2 Cloud Storage is often a good fit when:
Data needs to exist independently of a specific computer.
Multiple users or systems require access.
You need API-based access and automation.
You use third-party backup software that requires cloud object storage.
You need centralized storage for growing datasets.
You are building applications or data-driven workflows.
The focus isn’t on protecting a device. It’s on providing a durable, accessible home for data.
Understanding the data lifecycle
One reason organizations often use both backup and cloud storage is that data requirements change over time.
Consider a video production team.
While a project is actively being edited, the files may live on a workstation and several external drives. During that phase, protecting the editing environment is critical.
Once the project is complete, however, the priorities often change. The team may need to retain the content for future revisions, client requests, or compliance purposes. The files are no longer active, but they still need to remain available.
The same pattern appears across industries.
Architectural firms retain project files after construction is complete. Marketing teams archive campaign assets. Businesses preserve records for operational or regulatory reasons.
Not all data serves the same purpose throughout its lifecycle.
Active data often benefits from continuous endpoint protection, particularly when it lives on laptops, workstations, or attached drives. As that data ages, becomes shared across teams, or moves into long-term retention, cloud storage often becomes a more appropriate solution.
This is one reason many organizations use both Computer Backup and B2 Cloud Storage. The two solutions address different stages of the data lifecycle rather than competing for the same role.
When your storage requirements change
A common misconception is that organizations eventually “graduate” from backup to cloud storage. In reality, most environments become more complex over time, adding new requirements rather than replacing existing ones. As data volumes grow, teams collaborate across more systems, and retention needs increase, organizations often find themselves adding cloud storage to support those evolving demands. The shift isn’t typically about moving away from backup—it’s about addressing new use cases that emerge as data becomes more distributed, accessible, and valuable to the business. Common signs that additional cloud storage may make sense include:
Your data is no longer centered around one device
When multiple people need access to the same information, storing everything on a single workstation becomes limiting.
You’re building long-term archives
Completed projects, historical records, and large media libraries often benefit from dedicated cloud storage.
You’re adding automation and integrations
Applications, backup platforms, and workflows frequently require API-accessible storage.
You’re managing more than endpoints
As NAS devices, servers, and infrastructure become part of the environment, storage requirements often extend beyond individual computers.
In these scenarios, cloud storage isn’t replacing endpoint backup. It’s addressing new requirements.
The blind spot many cloud storage users discover
The reverse scenario is also common. An organization adopts cloud storage and establishes a centralized repository for important data, only to discover that important risks still exist at the endpoint level. An employee may accidentally delete a local project folder, lose a laptop, or experience a workstation failure before files have been synchronized elsewhere. Cloud storage protects the data stored in cloud storage, but it does not automatically protect every device where work is created. This is one reason endpoint backup remains an important part of many modern data protection strategies. The risks are different, and each solution is designed to address a different recovery scenario.
Why many organizations use both computer backup and cloud storage
One of the most persistent myths in data protection is that a single tool should solve every challenge. In practice, resilient environments are typically built in layers, with different solutions addressing different risks and recovery scenarios. Employee laptops may be protected with Computer Backup, while a NAS backs up to B2 Cloud Storage. Completed projects may be archived in the cloud while active work remains protected on local devices. Together, these layers create a more comprehensive approach to protecting data throughout its lifecycle.
Example: Creative teams
For creative teams, active projects often live on editing workstations and attached storage where they are constantly being updated. Computer Backup helps protect that work in progress, while completed projects can be moved to B2 Cloud Storage for long-term retention, future revisions, or client requests. This approach allows teams to safeguard current work without keeping every finished project on production systems.
Example: Growing businesses
As businesses grow, their data often becomes distributed across employee devices, shared storage, and business applications. Computer Backup can help protect employee endpoints where work is created, while B2 Cloud Storage provides a centralized location for shared assets, backups, and archives. Together, they support both day-to-day operations and longer-term data retention needs.
Example: IT and infrastructure teams
IT teams frequently manage a mix of endpoints, servers, NAS devices, and other business systems. In these environments, B2 Cloud Storage often serves as a destination for infrastructure backups, while Computer Backup protects employee devices that may not be covered by server or storage backup workflows. Rather than competing with one another, the two solutions often work together as part of a broader data protection strategy.
A quick comparison
Question
Computer Backup
B2 Cloud Storage
Is the primary goal protecting a computer?
Yes
No
Is it designed to protect endpoint data automatically?
Yes
No
Is the data primarily tied to a specific device?
Yes
Not necessarily
Is it designed for shared access across users, systems, or applications?
No
Yes
Is API access a core feature?
No
Yes
Can it serve as a destination for third-party backup tools?
No
Yes
Is the primary goal storing and managing cloud-resident data?
No
Yes
Choosing the right solution
The decision ultimately comes down to what you’re trying to protect and how your data is used.
If your primary concern is recovering files from a lost, stolen, damaged, or compromised computer, Computer Backup is likely the right starting point.
If you need scalable cloud storage for archives, applications, infrastructure backups, or shared datasets, B2 Cloud Storage is likely the better fit.
And if your environment includes both endpoints and cloud-resident data—as many organizations do—you may benefit from using both.
The most effective data protection strategies rarely rely on a single layer. They account for where data is created, where it lives, and how it needs to be recovered.
Understanding those requirements is often the first step toward choosing the right solution.
Backblaze Computer Backup was built on a simple promise: unlimited backup for everything on your computer. That promise hasn’t changed. But the way files live on your computer has, and we want to explain what’s happening, why it matters, and where we’re headed.
How cloud sync used to work
Not long ago, when you installed Dropbox or OneDrive, those apps copied your files directly onto your hard drive. They were real, local files. Backblaze would find them, back them up, and you could restore them just like anything else on your machine.
What changed
Over the past several years, cloud sync providers have fundamentally rearchitected how they store files at the operating system level. On Windows, tools like Dropbox and OneDrive now use something called the Cloud Files API, which represents your synced files as reparse points—essentially placeholders that point back to the cloud rather than storing actual data locally. The file appears to be there, but it’s really a redirect.
This isn’t a bad thing for those apps: it lets them sync efficiently and save local disk space. But it creates a real problem for backup software.
Why we can’t reliably back up placeholders
When Backblaze Computer Backup encounters a reparse point, we’re not looking at your file—we’re looking at a pointer. Backing that up wouldn’t actually protect your data; it would just save the redirect. And restoring a redirect isn’t a real restore. Since reliable backup and restore is the entire point, we made the decision to exclude folders managed this way rather than give customers a false sense of security.
This is also consistent with how we’ve always built the backup client: lightweight, unlimited, and focused on real user-generated files rather than duplicating data that already lives in the cloud.
Where we’ve made it work, and where we’re still working
We’ve successfully added support for iCloud Drive and Google Drive by working within those platforms’ models. Extending the same support to every sync provider is more complex, but it’s something we’re actively exploring.
Files where third-party tools have not added reparse points or other placeholder indicators and are stored directly on a customer’s computer, outside of third-party sync folders, continue to be backed up as they always have been. We are actively evaluating how to better support data from synced sources in the future.If you have questions about your current backup coverage, you can read our Docs about backing up third-party application data, or reach out to our Support team at [email protected].
In 2007, Backblaze started in a one-bedroom Palo Alto apartment. Since those days of hand-assembling Storage Pods, we’ve grown to manage over 5 exabytes of data for 500,000 customers across 175 countries. As our mission to make customers unstoppable grew, our team naturally grew with it, moving far beyond the walls of any single office.
The pandemic gave us the final piece of data we needed to evolve. When the world reopened, our San Mateo headquarters never quite looked the same. The office became a bit of a paradox: a large, quiet space where a handful of people moved through a space designed for hundreds. Meanwhile, the true heart and soul of the company was already thriving elsewhere, solving the world’s toughest storage challenges from data centers in Phoenix, spare bedrooms in Austin, and kitchen tables in Cheltenham.
We didn’t rush this. We experimented, explored, and really listened to our team. When we looked at the data, we found only around 5% of our teams worked out of the San Mateo office regularly. By testing new ways of collaborating, we confirmed what we already suspected: our culture isn’t tied to a physical floor plan, it’s tied to our shared commitment to our customers and each other. As of February 1, 2026, we made it official: Backblaze has moved beyond the hybrid model to become a fully remote, distributed company.
Listening, learning, and being practical
This transition isn’t about a grand corporate strategy, but about meeting our employees where they’re at—everywhere. While we appreciate the flexibility, we noticed that hybrid models can unintentionally create two different cultures, one for those who can make it into the office and another for everyone else. Whether an employee is in San Jose or the Philippines, we want them to have the same access to leadership, and each other. We’re now a team that finally matches the diversity and reach of the 175 countries we serve.
Beyond the culture, this is also about being good stewards of our financial resources. Holding onto an expensive, mostly empty office in one of the world’s costliest real estate markets was not a good investment. By letting go of the San Mateo office, we can more responsibly direct those investments toward our people—funding intentional collaboration tools, resources, and smaller local gatherings that strengthen connection and culture.
Let’s talk about the bedrock : Our data centers
While the “cloud” often feels like a metaphor, our Data Center Technicians know it’s built on hardware, precision, and physical presence. When it comes to data centers, there is no shifting the in-person work. Someone needs to be there to swap out a drive, and when it comes to making sure we’re always-on, that is a 24/7/365 commitment.
They are the heartbeat of Backblaze. Every day, they show up in person to the facilities where data actually lives, keeping the drives spinning to ensure that your data is always available and accessible.
Remote flexibility is a privilege afforded to the rest of the company by the physical excellence of our Data Center teams. They are the essential anchor that allows the rest of us to be weightless. We celebrate their work not as an exception to our model, but as the very foundation that makes our distributed future possible.
We’re still figuring it out
We are still finding new ways to connect. This isn’t a static policy, but a continuous effort to make sure people can be successful wherever they work. We’re replacing accidental hallway chats with deliberate rituals, from cross-functional coffee chats and regional off-sites with local talent and execs, to providing on-demand access to professional workspaces for solo work or we want to assemble together.
Closing the San Mateo office isn’t a retreat from our history; it’s an embrace of the company we’ve already become. As we grow across new markets and time zones, we’re committed to raising the bar on what distributed work can look like so our teams can collaborate in ways that drive real impact around the world. We are building a smarter, more intentional Backblaze, one that is as distributed as the data we protect and as resilient as the customers we serve.
Backblaze Computer Backup is designed to be simple: install it, and it runs in the background protecting data. For many businesses, that’s enough.
But, IT teams managing large deployments asked for more control over how backup is configured across their environments. We are now introducing two new tools built specifically for that need: Advanced Installer and the Backblaze Command Line Interface, bzcli.
What it does
The Advanced Installer gives IT teams a way to preconfigure and lock down certain client settings during rollout. That means when Backblaze is installed on an employee’s machine, it already has the company’s preferred settings in place—no need for end users to make adjustments.
Admins can:
Lock schedules so backups always run at the right time.
Manage exclusions centrally, avoiding the risk of someone skipping important folders.
Control security preferences to keep things consistent across the organization.
Suppress non-essential desktop notifications.
Instead of configuring machines individually or correcting settings after deployment, IT teams can define standards once and apply them consistently.
For organizations that frequently onboard employees, manage distributed teams, or provide backup as part of a managed service, this reduces variability and support overhead.
Bzcli: Remote configuration and reporting for RMM environments
In addition to the Advanced Installer, Backblaze Computer Backup will have access to bzcli, a new command-line interface designed for enterprise IT teams using RMM and MDM platforms.
Until now, Backblaze’s command-line support focused primarily on installation. Once deployed, there wasn’t a structured way for administrators to modify configuration settings or retrieve information remotely through automation tools. Bzcli addresses that gap.
Configure after installation
With bzcli, administrators can update client configuration settings after deployment using a structured JSON input file.
It supports the same settings available through the Advanced Installer and Preferences interface, including:
Backup schedules
Exclusions
Network controls
Security-related preferences
Notification behavior
This allows IT teams to adjust policies centrally without requiring user interaction.
Designed for automation
Bzcli uses a command-based structure (for example, bzcli configure and bzcli report) with clear flags and predictable output. It’s designed to work cleanly within scripts and automation workflows. The tool is cross-platform and included as part of the standard client installation on both Mac and Windows. It is intended to support environments using tools such as Jamf, Kandji, Addigy, and Microsoft Intune.
Why it matters
As organizations grow, consistency becomes more important. Backup policies need to be enforced reliably. Configuration drift creates risk. Unnecessary notifications create noise.
Advanced Installer and bzcli are designed to reduce that friction.
IT teams can define standards once, apply them consistently, and adjust them when needed, without manual intervention on individual machines.
For teams responsible for protecting company data across large environments, that added control makes deployment more predictable and ongoing management simpler.
Get started with a free 14-day trial of Backblaze Computer Backup today. Or, contact our Sales team to talk about your enterprise deployment today.
Mac admins have always understood the value of prioritizing Mac-native software to ensure performance and compatibility across their environments. With an integrated approach to data protection and device management from Backblaze and Kandji, you can now eliminate manual installations and deploy Backblaze with zero-touch across your entire Mac fleet, ensuring critical data is protected.
Simplifying Mac backup for remote and on-site IT teams
Whether your team is in the office or scattered across the globe, Backblaze’s cloud-based solution ensures your data is accessible and easily managed from anywhere.
Backblaze and Kandji’s solutions have already proven their value in Apple-focused IT environments.
Companies like Foojee, a managed IT provider specializing in Apple devices, rely on Kandji to deploy and manage those devices and Backblaze to protect their data. “We are always looking at best-of-breed apps for our customers, and we have never felt more proud of our product offering,” said Lucas Acosta, CEO of Foojee. “The three biggest benefits we have realized from Backblaze and Kandji are our time savings on our Help Desk, the increased security, and the increased reliability.”
This partnership builds on that success, enabling organizations to:
Deploy Backblaze effortlessly with Kandji: Automate installation and configuration of Backblaze on managed devices with Kandji’s workflows.
Enhance data security: Keep critical data protected with Backblaze’s secure, cloud-based backup service.
Scale with ease: Both platforms support organizations of any size, from startups to enterprises.
Reduce IT overhead: Streamline both device management and data protection with a unified platform.
Join the conversation
Interested in learning more? Join us on LinkedIn Live! Tune in for an in-depth discussion on how Backblaze and Kandji are helping organizations simplify and secure their Mac device management and data protection. Don’t miss out—save your spot today.
Get started
Interested in getting started? Contact our Sales team today to explore how Backblaze and Kandji can streamline your device management and data protection.
This post has been updated since it was originally published. Unfortunately, ransomware continues to proliferate. We’ve updated the post to reflect the current state of ransomware and to help individuals and businesses protect their data.
Ransomware is one of the biggest cybersecurity threats that businesses and organizations face today. Cybercriminals use these malicious attacks to encrypt an organization’s data and systems, holding them hostage and demanding a ransom for the encryption key. In the best case scenario, you can quickly restore from backups, but it’s a harrowing experience even when you’re well prepared. That’s why it makes sense to assume it’s not a question of if, but when, and plan accordingly.
With attacks becoming increasingly sophisticated and widespread, it’s crucial for businesses to have a comprehensive plan for ransomware prevention and recovery. In this guide, we’ll cover best practices for recovering your data and systems in the event of an attack, as well as proactive measures to strengthen your defenses against ransomware.
This post is a part of our ongoing coverage of ransomware. Take a look at our other posts for more information on how businesses can defend themselves against a ransomware attack, and more.
The statistics paint a cautionary picture—ransomware attacks are only getting more common. According to a 2023 Ransomware Market Report, global ransomware costs are predicted to reach $265 billion annually by 2031, up from $20 billion in 2021.
After a brief downturn in both incidents and payments in 2022, ransomware surged back in 2023. Ransomware complaints rose to over 2,825, marking an 18% increase from the previous year. And payments exceeded $1 billion, a 96% increase from the previous year, representing the highest number ever observed. What’s more, 59% of organizations were hit by ransomware in the last year, according to Sophos’ State of Ransomware 2024 report.
Cyber criminals are continuously evolving their strategies, with the FBI noting new trends such as deploying multiple ransomware variants against the same victim and employing data destruction tactics to intensify pressure on victims to negotiate.
Ransomware by the numbers
According to the Coveware Q1 2024 Quarterly Report, the ransomware landscape saw some notable shifts in ransom demand tactics. The report states that in the first quarter of 2024, the average ransom payment continued a downward trajectory, decreasing by 32% from Q4 2023 to $381,980. However, the median ransom payment increased by 25% to $250,000.
Coveware analysts suggest this divergence is driven by fewer companies paying exorbitant ransoms, which has a compounding effect on lowering the average payment amount. Concurrently, many ransomware groups are deliberately setting more reasonable initial ransom demands, aiming to keep victims engaged in negotiations rather than deterring them outright with astronomical figures. This new approach of “reasonably” priced ransoms is an intentional tactic to increase the likelihood of victims paying.
The same Coveware report provides insights into the widespread impact of ransomware across various industries. Healthcare emerged as the most targeted sector at 18.7%, followed closely by professional services at 17.8%. The public sector, including government and educational institutions, was also heavily impacted at 11.2%.
Other notable industries affected were consumer services (10.3%), retail (5.6%), financial services, and food & staples retail (both 4.7%). The data illustrates that ransomware is a pervasive threat cutting across diverse sectors, from critical infrastructure like healthcare to consumer businesses and technology firms.
No industry seems immune, as even traditionally less digitized fields like materials (6.5%), capital goods (2.8%), and automobile manufacturing (3.7%) suffered attacks. This underscores the need for robust cybersecurity measures and ransomware readiness plans across diverse organizations, regardless of their primary domain of operations.
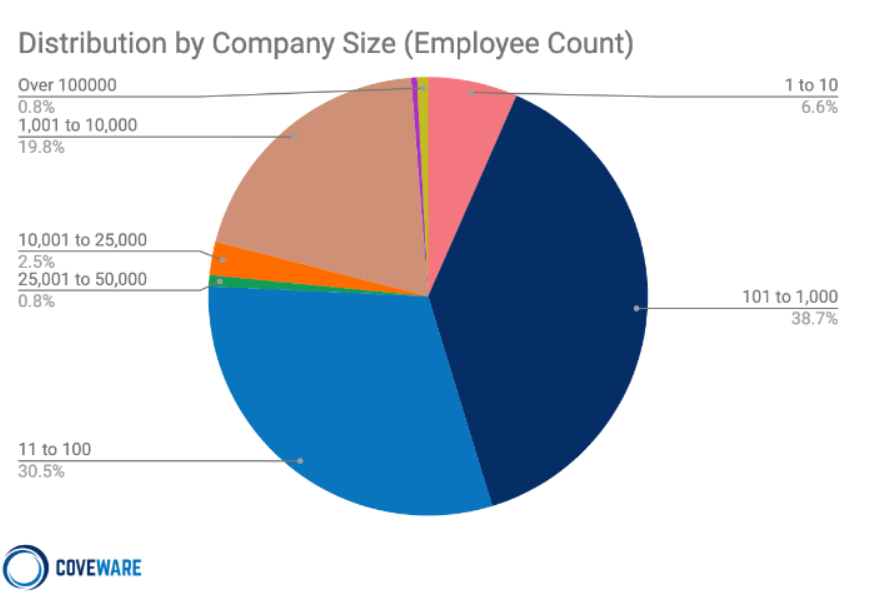
Ransomware also remains a significant threat across businesses of all sizes. However, small and medium sized businesses (SMBs) continue to bear the brunt of these attacks. A staggering 71.8% of impacted companies had between 11 and 1,000 employees, clearly demonstrating SMBs as a prime target for cybercriminals deploying ransomware.
While no organization is immune, the data highlights SMBs’ vulnerability, likely due to limited cybersecurity resources and staffing compared to larger enterprises. This highlights the critical need for SMBs to prioritize ransomware preparedness and implement robust security measures proportionate to the risks they face.
Simultaneously, the following chart indicates that ransomware groups are also setting their sights on major corporations, with 1.9% of impacted companies having over 100,000 employees. No sector can afford to be complacent about the pervasive ransomware threat landscape.
Ransomware as a service (Raas)
Ransomware as a service (RaaS) has emerged as a game changer in the world of cybercrime, revolutionizing the ransomware landscape and amplifying the scale and reach of malicious attacks. The RaaS business model allows even novice cybercriminals to access and deploy ransomware with relative ease, leading to a surge in the frequency and sophistication of ransomware attacks worldwide.
Traditionally, ransomware attacks required a high level of technical expertise and resources, limiting their prevalence to skilled cybercriminals or organized cybercrime groups. However, the advent of RaaS platforms has lowered the barrier to entry, making ransomware accessible to a broader range of individuals with nefarious intent. These platforms provide aspiring cybercriminals with ready-made ransomware toolkits, complete with user-friendly interfaces, step-by-step instructions, and even customer support. In essence, RaaS operates on a subscription or profit sharing model, allowing criminals to distribute ransomware and share the ransom payments with the RaaS operators.
The rise of RaaS has led to a proliferation of ransomware attacks, with cybercriminals exploiting the anonymity of the dark web to collaborate, share resources, and launch large scale campaigns. The RaaS model not only facilitates the distribution of ransomware, but it also provides criminals with analytics dashboards to track the performance of their campaigns, enabling them to optimize their strategies for maximum profit.
New strains and increased complexity
One of the most significant impacts of RaaS is the exponential growth in the number and variety of ransomware strains. RaaS platforms continuously evolve and introduce new ransomware variants, making it increasingly challenging for cybersecurity experts to develop effective countermeasures. The availability of these diverse strains allows cybercriminals to target different industries, geographical regions, and vulnerabilities, maximizing their chances of success.
The profitability of RaaS has attracted a new breed of cybercriminals, leading to an underground economy where specialized roles have emerged. Ransomware developers create and sell their malicious code on RaaS platforms, while affiliates or “distributors” spread the ransomware through various means, such as phishing emails, exploit kits, or compromised websites. This division of labor allows criminals to focus on their specific expertise, while RaaS operators facilitate the monetization process and collect a share of the ransoms.
Ransomware commoditization
The impact of RaaS extends beyond the immediate financial and operational consequences for targeted entities. The widespread availability of ransomware toolkits has also resulted in a phenomenon known as “ransomware commoditization,” where cybercriminals compete to offer their services at lower costs or even engage in price wars. This competition drives innovation and the continuous evolution of ransomware, making it a persistent and ever-evolving threat.
To combat the growing influence of RaaS, organizations and individuals require a multilayered approach to cybersecurity. Furthermore, organizations should prioritize data backups and develop comprehensive incident response plans to ensure quick recovery in the event of a ransomware attack. Regularly testing backup restoration processes is essential to maintain business continuity and minimize the impact of potential ransomware incidents.
RaaS has profoundly transformed the ransomware landscape, democratizing access to malicious tools and fueling the rise of cybercrime. The ease of use, scalability, and profitability of RaaS platforms have contributed to a surge in ransomware attacks across industries and geographic locations.
By staying vigilant and adopting robust cybersecurity measures, organizations can better protect themselves against the evolving threat posed by RaaS and ensure resilience in the face of potential ransomware incidents.
How does ransomware work?
A ransomware attack starts when a machine on your network becomes infected with malware. Cybercriminals have a variety of methods for infecting your machine, whether it’s an attachment in an email, a link sent via spam, or even through sophisticated social engineering campaigns. As users become more savvy to these attack vectors, cybercriminals’ strategies evolve. Once that malicious file has been loaded onto an endpoint, it spreads to the network, locking every file it can access behind strong encryption controlled by cybercriminals.
Types of ransomware, in addition to the traditional encryption model, include:
Non-encrypting ransomware or lock screens, which restrict access to files and data, but do not encrypt them.
Ransomware that encrypts a drive’s master boot record (MBR) or Microsoft’s NTFS, which prevents victims’ computers from being booted up in a live operating system (OS) environment.
Leakware or extortionware, which steals compromising or damaging data that the attackers then threaten to release if ransom is not paid. This type is on the rise—In 2023, 91% of ransomware attacks involved some sort of data exfiltration.
Mobile device ransomware which infects cell phones through drive-by downloads or fake apps.
What happens during a typical attack?
Threat actors have a lot of tools at their disposal to infiltrate systems, gather reconnaissance, and execute their mission. In cybersecurity parlance, these are called tactics, techniques, and procedures (TTPs). Without digging into too much detail, the typical lifecycle of a ransomware attack is as follows:
Initial compromise: Ransomware gains entry through various means such as exploiting known software vulnerabilities, using phishing emails or even physical media like thumb drives, brute-force attacks, and others. It then installs itself on a single endpoint or network device, granting the attacker remote access.
Secure key exchange: Once installed, the ransomware communicates with the perpetrator’s central command and control server, triggering the generation of cryptographic keys required to lock the system securely.
Encryption: With the cryptographic lock established, the ransomware initiates the encryption process, targeting files both locally and across the network, rendering them inaccessible without the decryption keys.
Extortion: Having gained secure and impenetrable access to your files, the ransomware displays an explanation of the next steps, including the ransom amount, instructions for payment, and the consequences of noncompliance.
Recovery options: At this stage, the victim can attempt to remove infected files and systems, restore from a clean backup, or some may consider paying the ransom.
It’s never advised to pay the ransom. According to Veeam’s 2024 Ransomware Trends Report, one in three organizations could not recover their data after paying the ransom. There’s no guarantee the decryption keys will work, and paying the ransom only further incentivizes cybercriminals to continue their attacks.
Who gets attacked?
Data has shown that ransomware attacks target firms of all sizes, and no business—from SMBs to large corporations—is immune. Attacks are on the rise in every sector and in every size of business. That said, small to medium-sized businesses are particularly vulnerable, as they may not have the resources needed to shore up their defenses and are often viewed as “easy targets” by cybercriminals.
Recent attacks where cybercriminals leaked sensitive photos of patients in a medical facility prove that no organization is out of bounds and no victim is off-limits. These attempts indicate that organizations which often have weaker controls and out-of-date or unsophisticated IT systems should take extra precautions to protect themselves and their data (especially their backup data!).
According to Veeam’s report, backup repositories are a prime target for bad actors. In fact, backup repositories are targeted in 96% of attacks, with bad actors successfully affecting the backup repositories in 76% of cases.
The U.S. consistently ranks highest in ransomware attacks, followed by the U.K. and Germany. Windows computers are the main targets, but ransomware strains exist for Macintosh and Linux, as well.
The unfortunate truth is that ransomware has become so widespread that most companies will certainly experience some degree of a ransomware or malware attack. The best they can do is be prepared and understand the best ways to minimize the impact of ransomware.
Backup repositories are targeted in 96% of attacks.
How to combat ransomware
So, you’ve been attacked by ransomware. Depending on your industry and legal requirements (which are ever-changing), you may be obligated to report the attack immediately. Otherwise, your footing should be one of damage control. What should you do next?
Isolate the infection. Swiftly isolate the infected endpoint from the rest of your network and any shared storage to halt the spread of the ransomware.
Identify the infection. With numerous ransomware strains in existence, it’s crucial to accurately identify the specific type you’re dealing with. Conduct scans of messages, files, and utilize identification tools to gain a clearer understanding of the infection.
Report the incident. While legal obligations may vary, it is advisable to report the attack to the relevant authorities. Their involvement can provide invaluable support and coordination for countermeasures.
Evaluate your options. Assess the available courses of action to address the infection. Consider the most suitable approach based on your specific circumstances.
Restore and rebuild. Utilize secure backups, trusted program sources, and reliable software to restore the infected systems or set up a new system from scratch.
1. Isolate the infection
Depending on the strain of ransomware you’ve been hit with, you may have little time to react. Fast-moving strains can spread from a single endpoint across networks, locking up your data as it goes, before you even have a chance to contain it.
The first step, even if you just suspect that one computer may be infected, is to isolate it from other endpoints and storage devices on your network. Disable Wi-Fi, disable Bluetooth, and unplug the machine from both any local area network (LAN) or storage device it might be connected to. This not only contains the spread but also keeps the ransomware from communicating with the attackers.
Know that you may be dealing with more than just one “patient zero.” The ransomware could have entered your system through multiple vectors, particularly if someone has observed your patterns before they attacked your company. It may already be laying dormant on another system. Until you can confirm, treat every connected and networked machine as a potential host to ransomware.
2. Identify the infection
Just as there are bad guys spreading ransomware, there are good guys helping you fight it. Sites like ID Ransomware and the No More Ransom! Project help identify which strain you’re dealing with. And knowing what type of ransomware you’ve been infected with will help you understand how it propagates, what types of files it typically targets, and what options, if any, you have for removal and disinfection. You’ll also get more information if you report the attack to the authorities (which you really should).
3. Report to the authorities
It’s understood that sometimes it may not be in your business’s best interest to report the incident. Maybe you don’t want the attack to be public knowledge. Maybe the potential downside of involving the authorities (lost productivity during investigation, etc.) outweighs the amount of the ransom. But reporting the attack is how you help everyone avoid becoming victimized and help combat the spread and efficacy of ransomware attacks in the future. With every attack reported, the authorities get a clearer picture of who is behind attacks, how they gain access to your system, and what can be done to stop them.
The good news is, you have options. The bad news is that the most obvious option, paying up, is a terrible idea.
Simply giving into cybercriminals’ demands may seem attractive to some, especially in those previously mentioned situations where paying the ransom is less expensive than the potential loss of productivity. Cybercriminals are counting on this.
However, paying the ransom only encourages attackers to strike other businesses or individuals like you. Paying the ransom not only fosters a criminal environment but also leads to civil penalties—and you might not even get your data back.
The other option is to try and remove it, or to start over.
5. Restore and rebuild—or start fresh
There are several sites and software packages that can potentially remove the ransomware from your system, including the No More Ransom! Project. Other options can be found, as well.
Whether you can successfully and completely remove an infection is up for debate. A working decryptor doesn’t exist for every known ransomware. The nature of the beast is that every time a good guy comes up with a decryptor, a bad guy writes new ransomware. To be safe, you’ll want to follow up by either restoring your system or starting over entirely.
Why starting over using your backups is the better idea
The surest way to confirm ransomware has been removed from a system is by doing a complete wipe of all storage devices and reinstalling everything from scratch. Formatting the hard disks in your system will ensure that no remnants of the ransomware remain.
To effectively combat the ransomware that has infiltrated your systems, it is crucial to determine the precise date of infection by examining file dates, messages, and any other pertinent information. Keep in mind that the ransomware may have been dormant within your system before becoming active and initiating significant alterations. By identifying and studying the specific characteristics of the ransomware that targeted your systems, you can gain valuable insights into its functionality, enabling you to devise the most effective strategy for restoring your systems to their optimal state.
A concerning 63% of organizations hastily restore directly back into compromised production environments without adequate scanning during recovery, risking re-introduction of the threat.
Select a backup or backups that were made prior to the date of the initial ransomware infection. If you’ve been following a sound backup strategy, you should have copies of all your documents, media, and important files right up to the time of the infection. With both local and off-site backups, you should be able to use backup copies that you know weren’t connected to your network after the time of attack, and hence, protected from infection. However, it is recommended to use a secure quarantine environment for testing before bringing production systems back online to ensure there is no dormant ransomware present in the data before restoring to production systems.
How Object Lock protects your backups
Object Lock functionality for backups allows you to store objects using a write once, read many (WORM) model, meaning that after it’s written, data cannot be modified. Using Object Lock, no one can encrypt, tamper with, or delete your protected data for a specified period of time, creating a solid line of defense against ransomware attacks.
Object Lock creates a virtual air gap for your data. The term “air gap” comes from the world of LTO tape. When backups are written to tape, the tapes are then physically removed from the network, creating a literal gap of air between backups and production systems. In the event of a ransomware attack, you could just pull the tapes from the previous day to restore systems. Object Lock does the same thing, but it all happens in the cloud. Instead of physically isolating data, Object Lock virtually isolates the data.
Object Lock is valuable in a few different use cases:
To replace an LTO tape system: Most folks looking to migrate from tape are concerned about maintaining the security of the air gap that tape provides. With Object Lock, you can create a backup that’s just as secure as air-gapped tape without the need for expensive physical infrastructure.
To protect and retain sensitive data: If you work in an industry that has strong compliance requirements—for instance, if you’re subject to HIPAA regulations or if you need to retain and protect data for legal reasons—Object Lock allows you to easily set appropriate retention periods to support regulatory compliance.
As part of a disaster recovery (DR) and business continuity plan: The last thing you want to worry about in the event you are attacked by ransomware is whether your backups are safe. Being able to restore systems from backups stored with Object Lock can help you minimize downtime and interruptions, comply with cyber insurance requirements, and achieve recovery time objectives (RTO) easier. By making critical data immutable, you can quickly and confidently restore uninfected data from your backups, deploy them, and return to business without interruption.
Ransomware attacks can be incredibly disruptive. By adopting the practice of creating immutable, air-gapped backups using Object Lock functionality, you can significantly increase your chances of achieving a successful recovery. This approach brings you one step closer to regaining control over your data and mitigating the impact of ransomware attacks.
So, why not just run a system restore?
While it might be tempting to rely solely on a system restore point to restore your system’s functionality, it is not the best solution for eliminating the underlying virus or ransomware responsible for the initial problem. Malicious software tends to hide within various components of a system, making it impossible for system restore to eradicate all instances.
Another critical concern is that ransomware has the capability to infect and encrypt local backups. If a computer is infected with ransomware, there is a high likelihood that your local backup solution will also suffer from data encryption, just like everything else on the system.
With a good backup solution that is isolated from your local computers, you can easily obtain the files you need to get your system working again. This will also give you the flexibility to determine which files to restore from a particular date and how to obtain the files you need to restore your system.
Initial compromise TTPs: Human attack vectors
Often, the weak link in your security protocol is the ever-elusive X factor of human error. Cybercriminals know this and exploit it through social engineering. In the context of information security, social engineering is the use of deception to manipulate individuals into divulging confidential or personal information that may be used for fraudulent purposes. In other words, the weakest point in your system is usually somewhere between the keyboard and the chair.
Common human attack vectors include:
1. Phishing
Phishing uses seemingly legitimate emails to trick people into clicking on a link or opening an attachment, unwittingly delivering the malicious payload. The email might be sent to one person or many within an organization, but sometimes the emails are targeted to help them seem more credible. This targeting takes a little more time on the attackers’ part, but the research into individual targets can make their email seem even more legitimate, not to mention the assistance of generative AI models like ChatGPT. They might disguise their email address to look like the message is coming from someone the sender knows, or they might tailor the subject line to look relevant to the victim’s job. This highly personalized method is called “spear phishing.”
2. SMSishing
As the name implies, SMSishing uses text messages to get recipients to navigate to a site or enter personal information on their device. Common approaches use authentication messages or messages that appear to be from a financial or other service provider. Even more insidiously, some SMSishing ransomware variants attempt to propagate themselves by sending themselves to all contacts in the device’s contact list.
3. Vishing
In a similar manner to email and SMS, vishing uses voicemail to deceive the victim, leaving a message with instructions to call a seemingly legitimate number which is actually spoofed. Upon calling the number, the victim is coerced into following a set of instructions which are ostensibly to fix some kind of problem. In reality, they are being tricked into installing ransomware on their own computer. Like so many other methods of phishing, vishing has become increasingly sophisticated with the spread of AI, with recent, successful deepfakes leveraging vishing to duplicate the voices of company higher-ups—to the tune of $25 million. And like spear phishing, it has become highly targeted.
4. Social media
Social media can be a powerful vehicle to convince a victim to open a downloaded image from a social media site or take some other compromising action. The carrier might be music, video, or other active content that, once opened, infects the user’s system.
5. Instant Messaging
Between them, IM services like WhatsApp, Facebook Messenger, Telegram, and Snapchat have more than four billion users, making them an attractive channel for ransomware attacks. These messages can seem to come from trusted contacts and contain links or attachments that infect your machine and sometimes propagate across your contact list, furthering the spread.
Ransomware is more about manipulating vulnerabilities in human psychology than the adversary’s technological sophistication.”
—James Scott, Institute for Critical Infrastructure Technology
Initial compromise TTPs: Machine attack vectors
The other type of attack vector is machine to machine. Humans are involved to some extent, as they might facilitate the attack by visiting a website or using a computer, but the attack process is automated and doesn’t require any explicit human cooperation to invade your computer or network.
1. Drive-by
The drive-by vector is particularly malicious, since all a victim needs to do is visit a website carrying malware within the code of an image or active content. As the name implies, all you need to do is cruise by and you’re a victim.
2. Known system vulnerabilities
Cybercriminals learn the vulnerabilities of specific systems and exploit those vulnerabilities to break in and install ransomware on the machine. This happens most often to systems that are not patched with the latest security releases.
3. Malvertising
Malvertising is like drive-by, but uses ads to deliver malware. These ads might be placed on search engines or popular social media sites in order to reach a large audience. A common host for malvertising is adults-only sites.
4. Network propagation
Once a piece of ransomware is on your system, it can scan for file shares and accessible computers and spread itself across the network or shared system. Companies without adequate security might have their company file server and other network shares infected as well. From there, the malware will propagate as far as it can until it runs out of accessible systems or meets security barriers.
5. Propagation through shared services
Online services such as file sharing or syncing services can be used to propagate ransomware. If the ransomware ends up in a shared folder on a home machine, the infection can be transferred to an office or to other connected machines. If the service is set to automatically sync when files are added or changed, as many file sharing services are, then a malicious virus can be widely propagated in just milliseconds.
It’s important to be careful and consider the settings you use for systems that automatically sync, and to be cautious about sharing files with others unless you know exactly where they came from.
Prevention best practices
Security experts suggest several precautionary measures for preventing a ransomware attack.
Use antivirus and antimalware software or other security policies to block known payloads from launching.
Make frequent, comprehensive backups of all important files and isolate them from local and open networks.
Immutable backup options such as Object Lock offer users a way to maintain truly air-gapped backups. The data is fixed, unchangeable, and cannot be deleted within the time frame set by the end user.
Keep offline data backups stored in locations that are air gapped or inaccessible from any potentially infected computer, such as on disconnected external storage drives or in the cloud, which prevents the ransomware from accessing them.
Keep your security up-to-date through trusted vendors of your OS and applications. Remember to patch early and patch often to close known vulnerabilities in operating systems, browsers, and web plugins.
Consider deploying security software to protect endpoints, email servers, and network systems from infection.
Segment your networks to keep critical computers isolated and to prevent the spread of ransomware in case of an attack. Turn off unneeded network shares.
Operate on the principle of least privilege. Turn off admin rights for users who don’t require them. Give users the lowest system permissions they need to do their work.
Restrict write permissions on file servers as much as possible.
Educate yourself and your employees in best practices to keep ransomware out of your systems. Update everyone on the latest email phishing scams and human engineering aimed at turning victims into abettors.
It’s clear that the best way to respond to a ransomware attack is to avoid having one in the first place. Other than that, making sure your valuable data is backed up and unreachable to a ransomware infection will ensure that your downtime and data loss will be minimal if you ever fall prey to an attack.
Have you endured a ransomware attack or have a strategy to keep you from becoming a victim? Please let us know in the comments.
Ransomware FAQS
What is a ransomware attack?
A ransomware attack is a type of cyberattack where cybercriminals or groups gain access to a computer system or network and encrypt valuable files or data, making them inaccessible to the owner. The attackers then demand a ransom, usually in the form of cryptocurrency, in exchange for providing the decryption key to unlock the files. Attackers may also extort victims by exfiltrating and threatening to leak sensitive data. Ransomware attacks can cause significant financial losses, operational disruptions, and potential data breaches if the ransom is not paid or effective countermeasures are not implemented.
How do I prevent ransomware attacks?
Preventing ransomware requires a proactive approach to cybersecurity and cyber resilience. Implement robust security measures, including regularly updating software and operating systems, utilizing strong and unique passwords, and deploying reputable antivirus and antimalware software. Train employees about how to identify phishing and social engineering tactics. Regularly back up critical data to cloud storage, implement tools like Object Lock to create immutability, and test your restoration processes. Lastly, stay informed about the latest threats and security best practices to fortify your defenses against ransomware.
How does ransomware work?
Ransomware gains entry through various means such as phishing emails, physical media like thumb drives, or alternative methods. It then installs itself on one or more endpoints or network devices, granting the attacker access. Once installed, the ransomware communicates with the perpetrator’s central command and control server, triggering the generation of cryptographic keys required to lock the system securely. With the cryptographic lock established, the ransomware initiates the encryption process, targeting files both locally and across the network, and renders them inaccessible without the decryption keys.
How does ransomware spread?
Common ransomware attack vectors include malicious email attachments or links, where users unknowingly download or execute the ransomware payload. It can also spread through exploit kits that target vulnerabilities in software or operating systems. Ransomware may propagate through compromised websites, drive-by downloads, or via malicious ads. Additionally, attackers can utilize brute force attacks to gain unauthorized access to systems and deploy ransomware.
How do I recover from a ransomware attack?
First, contain the infection. Isolate the infected endpoint from the rest of your network and any shared storage. Next, identify the infection. With numerous ransomware strains in existence, it’s crucial to accurately identify the specific type you’re dealing with. Conduct scans of messages, files, and utilize identification tools to gain a clearer understanding of the infection. Report the incident. While legal obligations may vary, it is advisable to report the attack to the relevant authorities. Their involvement can provide invaluable support and coordination for countermeasures. Then, assess the available courses of action to address the infection. If you have a solid backup strategy in place, you can utilize secure backups to restore and rebuild your environment.
Image credits below: Mason Cummings, The Wilderness Society.
Saving the environment is one of the most noble tasks anyone can undertake, but the thing about the environment is that it’s notoriously rough on laptops.
For the staff of The Wilderness Society, saving wild places means trekking out into said wild with boots firmly on the ground. Whether that means shutting down copper mines that would have otherwise devastated nearby waterways or helping create public transportation routes out to public lands, The Wilderness Society is a group constantly on the move. That doesn’t leave a lot of time for dealing with backups, particularly in the geographically far-flung areas in which The Wilderness Society researchers find themselves.
Data saved on staff laptops was regularly at risk, and The Wilderness Society needed a way to protect that data from threats both natural and otherwise. Director of Information Technology, Kristin Iden, shared how she:
Protected essential workstation data with cloud backups.
Achieved a security stance that aligns with cyber insurance policies.
Eased the administrative burden on an IT team of two that serves more than 160 staff around the country.
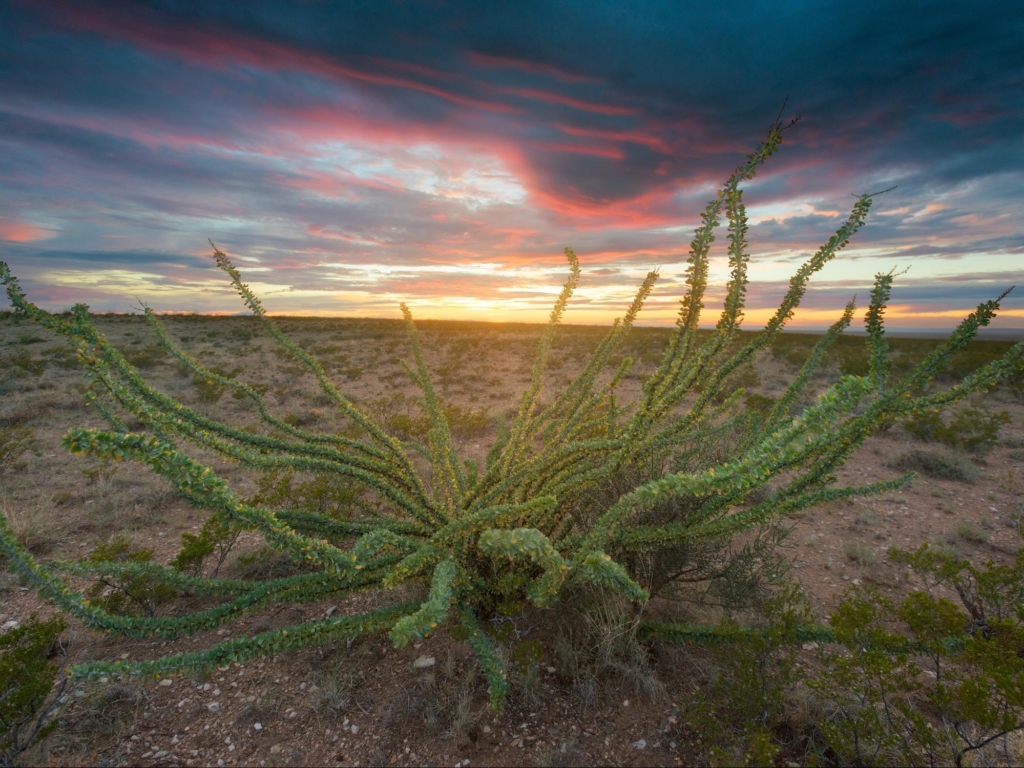
Otero Mesa, New Mexico.
The Wilderness Society: A Force for Change
Since 1935, The Wilderness Society has led the effort to permanently protect 109 million acres of wilderness in 44 states. They have been at the forefront of nearly every major public lands victory. Initiatives include climate change solutions, land and water conservation, and community-led conservation.
How Workstation Backups Protect Data From Disasters
The urgency to put a solid workstation backup plan in place hit home for Kristin when her laptop was destroyed by a lightning strike. And yes, she’s aware of the irony. The IT director, one of the few who isn’t dragging their laptop across creation, is the one who lost data to natural disaster.
The Wilderness Society’s researchers find themselves all over the world as part of their mission to protect the environment. There are 14 offices from coast to coast, from Hallowell, Maine to Anchorage, Alaska. According to Kristin, “drop and destroy” events are not uncommon out in the field, whether it’s a laptop taking an accidental trip down a mountainside or into the waters of the Arctic Circle.
Add to that, as a nonprofit organization, The Wilderness Society always has to look at the bottom line. Their funding comes entirely from donors and sponsors, gifted with a purpose, and as much of it should go toward the mission as possible. In fact, Kristin had originally sought out a backup solution solely for executives as a way to save budget, but Backblaze’s affordability made it a no-brainer to extend backups out into the field.
“If somebody in the Arctic Circle drops and breaks their laptop, now I can get them back up and running within a couple of days. ”
—Kristin Iden, Director of Information Technology, The Wilderness Society
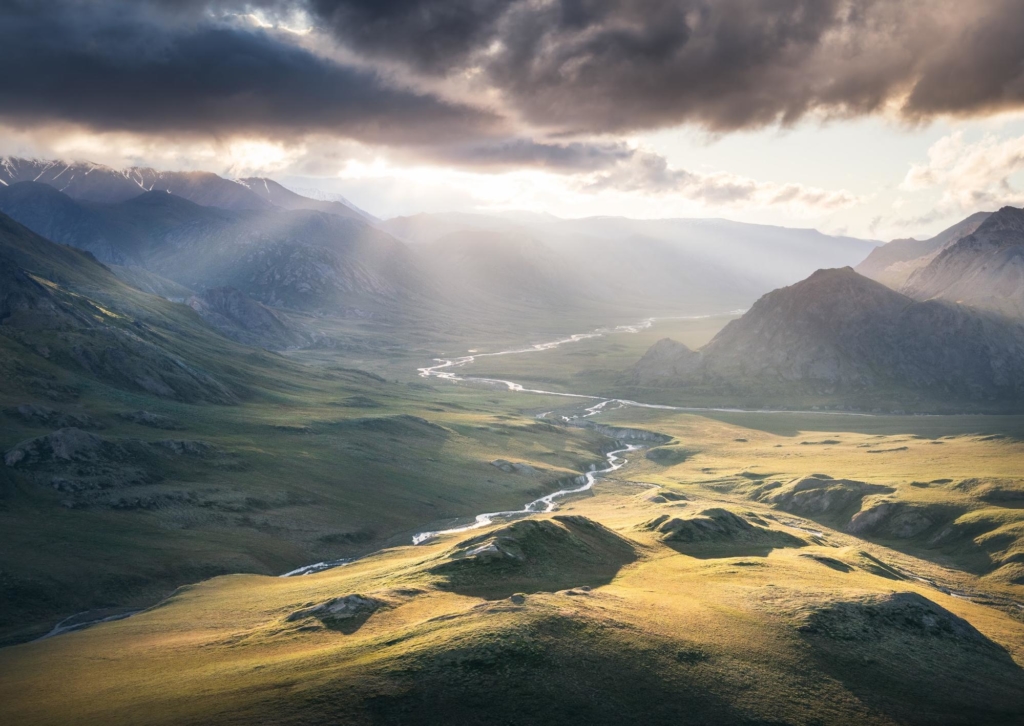
Arctic National Wildlife Refuge, Alaska.
How to Back Up Field Staff Workstations
Kristin started with a beta test group of around 10% of the users, making sure to include a mix of field researchers, administrative workers, and executives. One important group to include in this mix was the handful of workers in truly remote regions of the country that have metered bandwidth. This obviously made regular backups difficult, but Kristin found a workaround by having them run the backup during weekly office visits.
The two members of the IT department are the sole administrators on the roughly 160 machines throughout the organization, an 80/20 mix of PC and Mac users. As such, they were able to roll out installation of Backblaze through Microsoft Intune, a mass deployment tool. The initial beta test went off without a hitch, and they took a phased approach to the remaining rollout—Backblaze was installed across the entire organization in groups of 30.
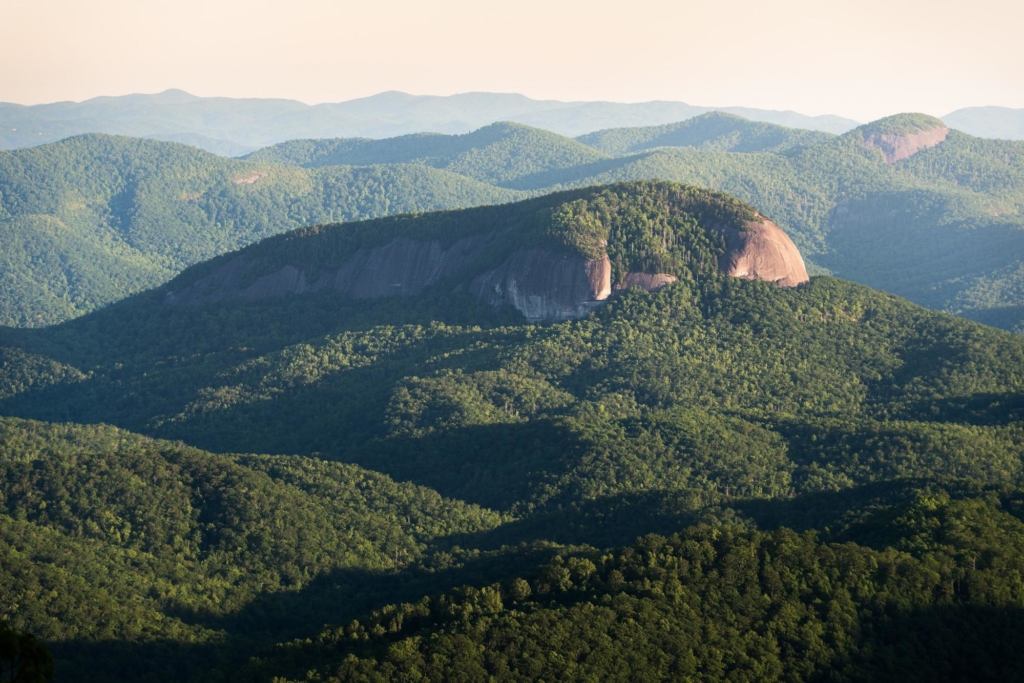
Pisgah National Forest, North Carolina.
Lightweight Backup Client Provides Peace of Mind
Kristin knew there was simply no way to prevent the inevitable destruction of user laptops out in the field. By focusing her efforts on finding the right backup solution, she was able to easily roll out to the entire organization a solution that protected their data from the rigors of nature.
Of paramount importance was simplifying the entire process for the users. They are, after all, doing the truly critical work of protecting the environment. Whether that means surveying wildlife in their native environment or working with lawmakers to craft bills that preserve nature, Kristin wanted their focus on the mission and not on their machine. With a lightweight client that doesn’t bog down machines and reliable backups she can use to provision new machines and recover data, Backblaze gave her that turnkey solution, and the peace of mind that followed.
“Admin tasks like backups are a time suck when you’re a two-person team minding 160 people running around the country trying to make sure the forests stay up. I don’t have time to babysit something constantly. With Backblaze, it just does its thing, and it lets me know when something’s not working. That’s exactly what I want out of every tool I use—just work, tell me when it isn’t, and make it easy to fix it. Backblaze just works everywhere we need it to.”
—Kristin Iden, Director of Information Technology, The Wilderness Society
With CrashPlan sunsetting its On-Premises backup service as of February 28, 2022, customers have some choices to make about how to handle their backups moving forward. As you think about the options—all of which require IT managers to embrace a change—we’d be remiss if we didn’t say Backblaze is ready to help with our Business Backup service for workstations. It’s quick and easy to switch over to, easy to run automatically ongoing, and cost effective.
If you’re a CrashPlan customer but you need a new backup solution, read on to understand your options. If you’re interested in working with us, you can transition from CrashPlan to Backblaze in six simple steps outlined below to protect all employee workstations from accidental data loss or ransomware, automatically and affordably.
What Options Do CrashPlan Customers Have?
CrashPlan customers have two options: transfer to CrashPlan’s Cloud Backup Service or transfer to another vendor. CrashPlan customers have until March 1, 2022 to make the decision and get started. After March 1, CrashPlan customers will lose support for their backup software. If any issues arise with backing up or restoring data, you won’t receive support to help fix the situation from CrashPlan.
CrashPlan’s Cloud Backup Service starts at $10 per endpoint per month for 0-100 endpoints, and is tiered after that. For customers looking for different pricing options or features, some CrashPlan alternatives include Carbonite and iDrive, both of which are offering promotions to attract CrashPlan customers. Keep in mind that once these promotions expire, you’re stuck paying the full price which may be higher than others. And, of course, Backblaze is an option as well.
Transferring from CrashPlan to Backblaze
So, what makes Backblaze a great fit for CrashPlan customers? We’ll share a few reasons. If you are already convinced, you can get started now by following the getting started guide in the next section of this post. If not, here are some of the benefits you’ll get with Backblaze:
Unlimited and Automatic: Lightweight Mac and PC clients back up all user data by default and are Java-free for stability—no system slow-downs or crashes.
Easy Admin and Restores: Transition in a few simple steps then easily manage and deploy at scale via a centralized admin console by choosing from a number of mass-deployment tools with multiple restore options.
Affordable and Predictable: Protect all employee workstations for just $70/computer, with no surprise charges, plus monthly, yearly, or two-year billing flexibility to suit your needs.
Safe and Secure: Defend your business data from ransomware and other threats with single sign-on, two-factor authentication, encryption at rest, encryption in transit, and ransomware protection.
Live Support: Make your transition easy with support during your transition and deployment via our customer service team and solution engineers.
Backblaze has been in the backup business for 15 years, and businesses ranging from PagerDuty to Charity: Water to Roush Auto Group rely on us for their data protection. Former CrashPlan customers who recently transitioned to Backblaze are getting the value they expected. Recently, Richard Charbonneau of Clicpomme spoke of the ease and simplicity he gained from switching:
“All our clients are managed by MDM or Munki, so it was really easy for us just to push the uninstaller for CrashPlan and package the new installer for Backblaze for every client.”
– Richard Charbonneau, Founder, Clicpomme
We invite you to join them.
Ready to Get Started?
How to Transition to Backblaze: Getting Started
You can “version off” of CrashPlan and “version on” to Backblaze Business Backup, making for a seamless transition. Simply create and configure an account with Backblaze to start backing up all employee workstations, and let CrashPlan lapse when they sunset On-Premises support on February 28.
You can retain your CrashPlan backups on premises for however long your retention policies stipulate in case you need to restore (or just deprecate those altogether if you’d rather use your on-premises storage servers for something else—it’s up to you!). Then, with Backblaze set up in parallel, you can start relying on Backblaze moving forward.
Here’s how to get started with Backblaze Business Backup.
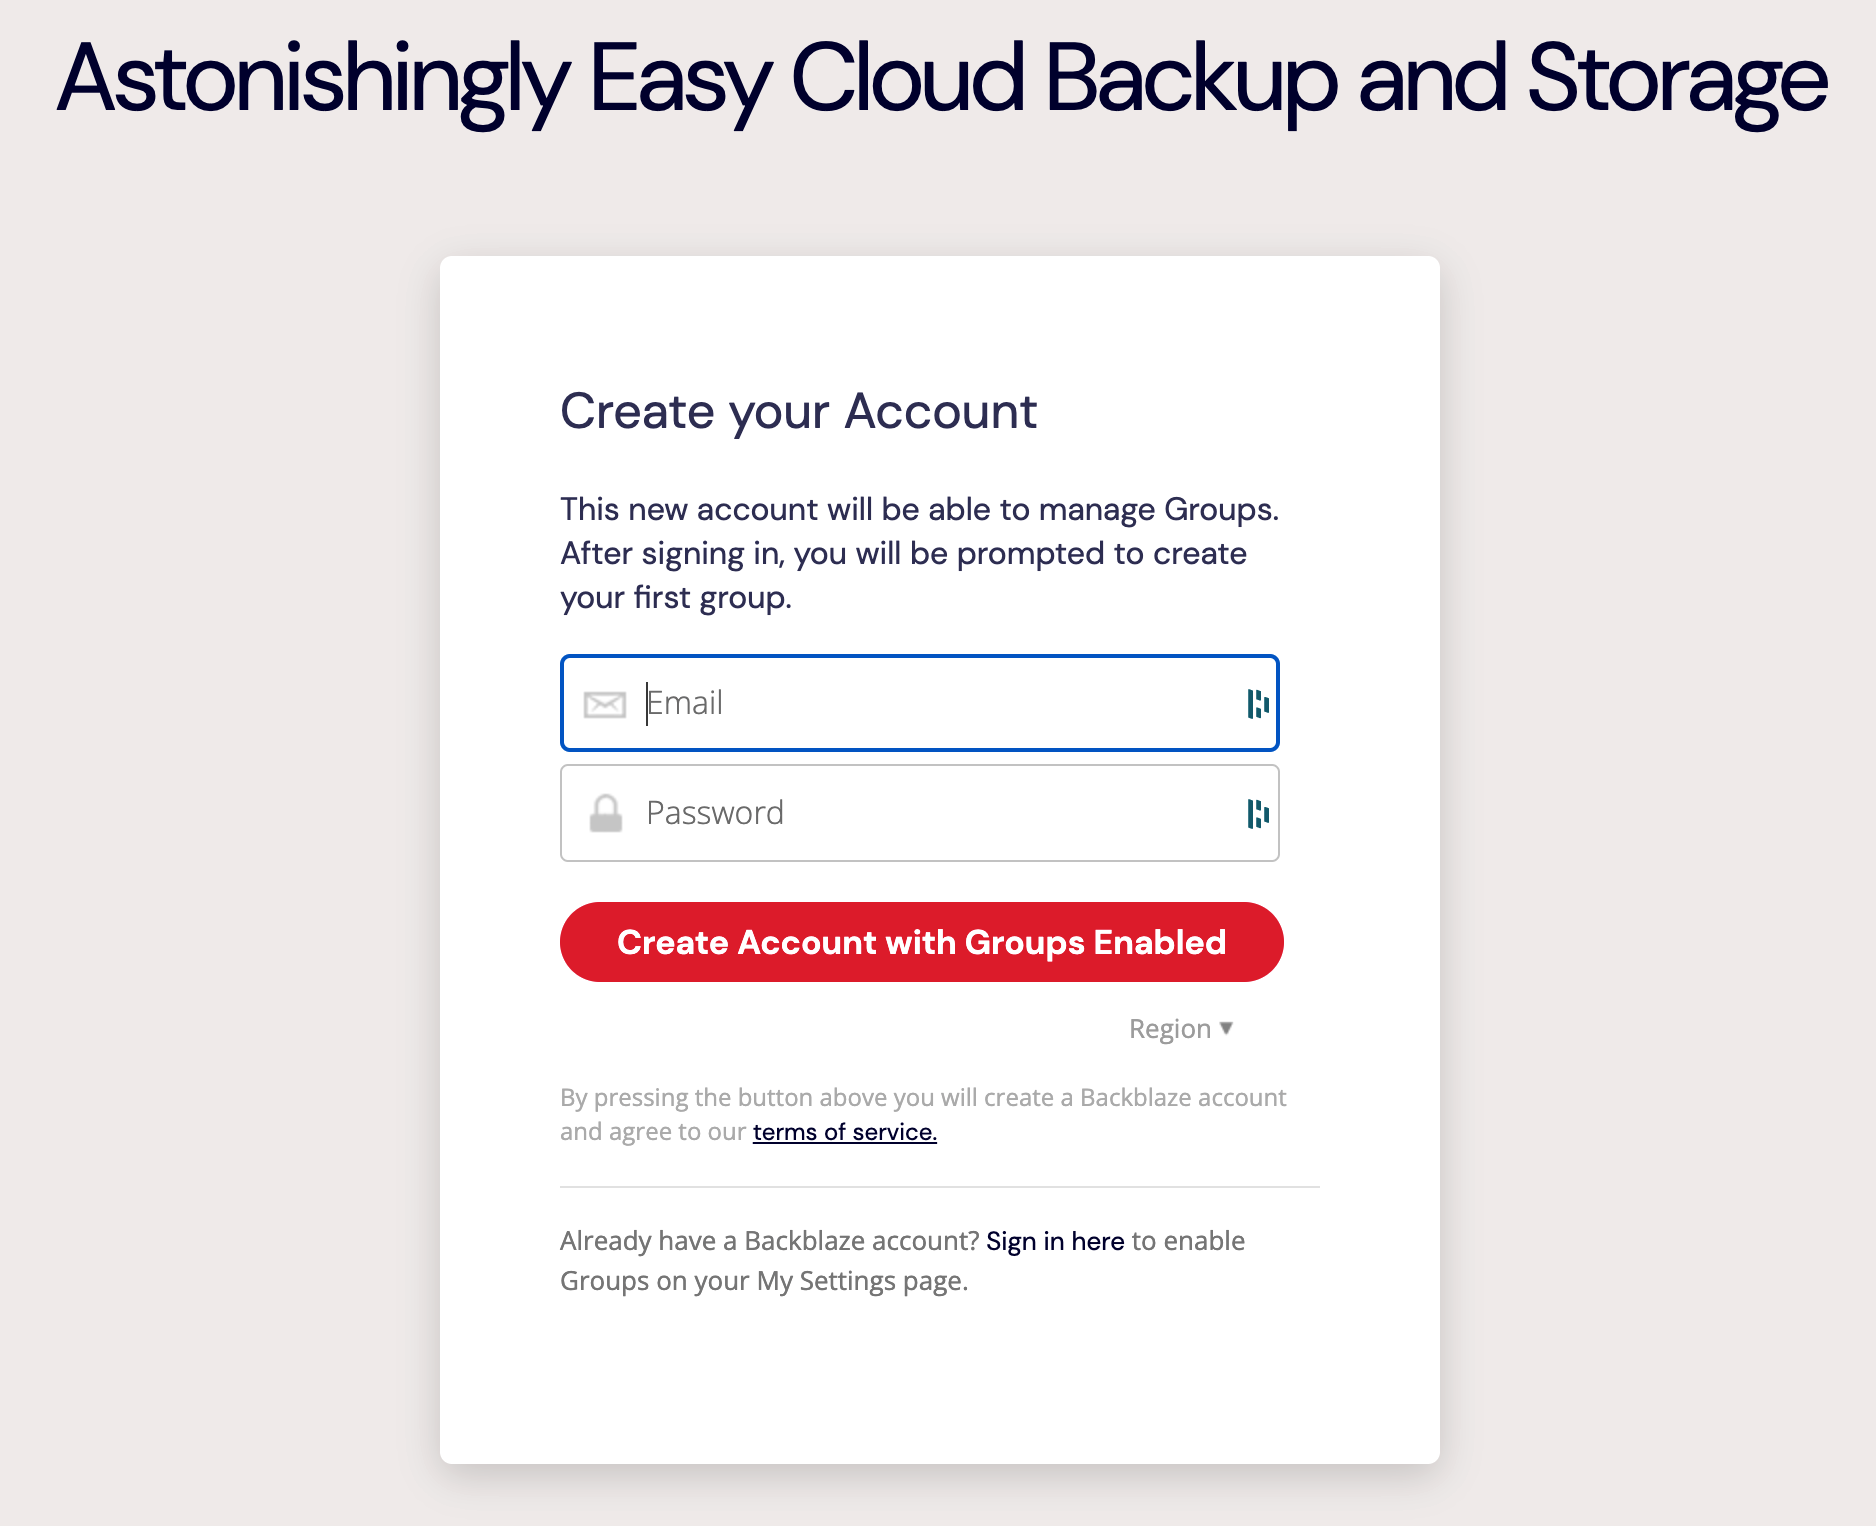
Enter an email address and password. Then click Create Account with Groups Enabled.
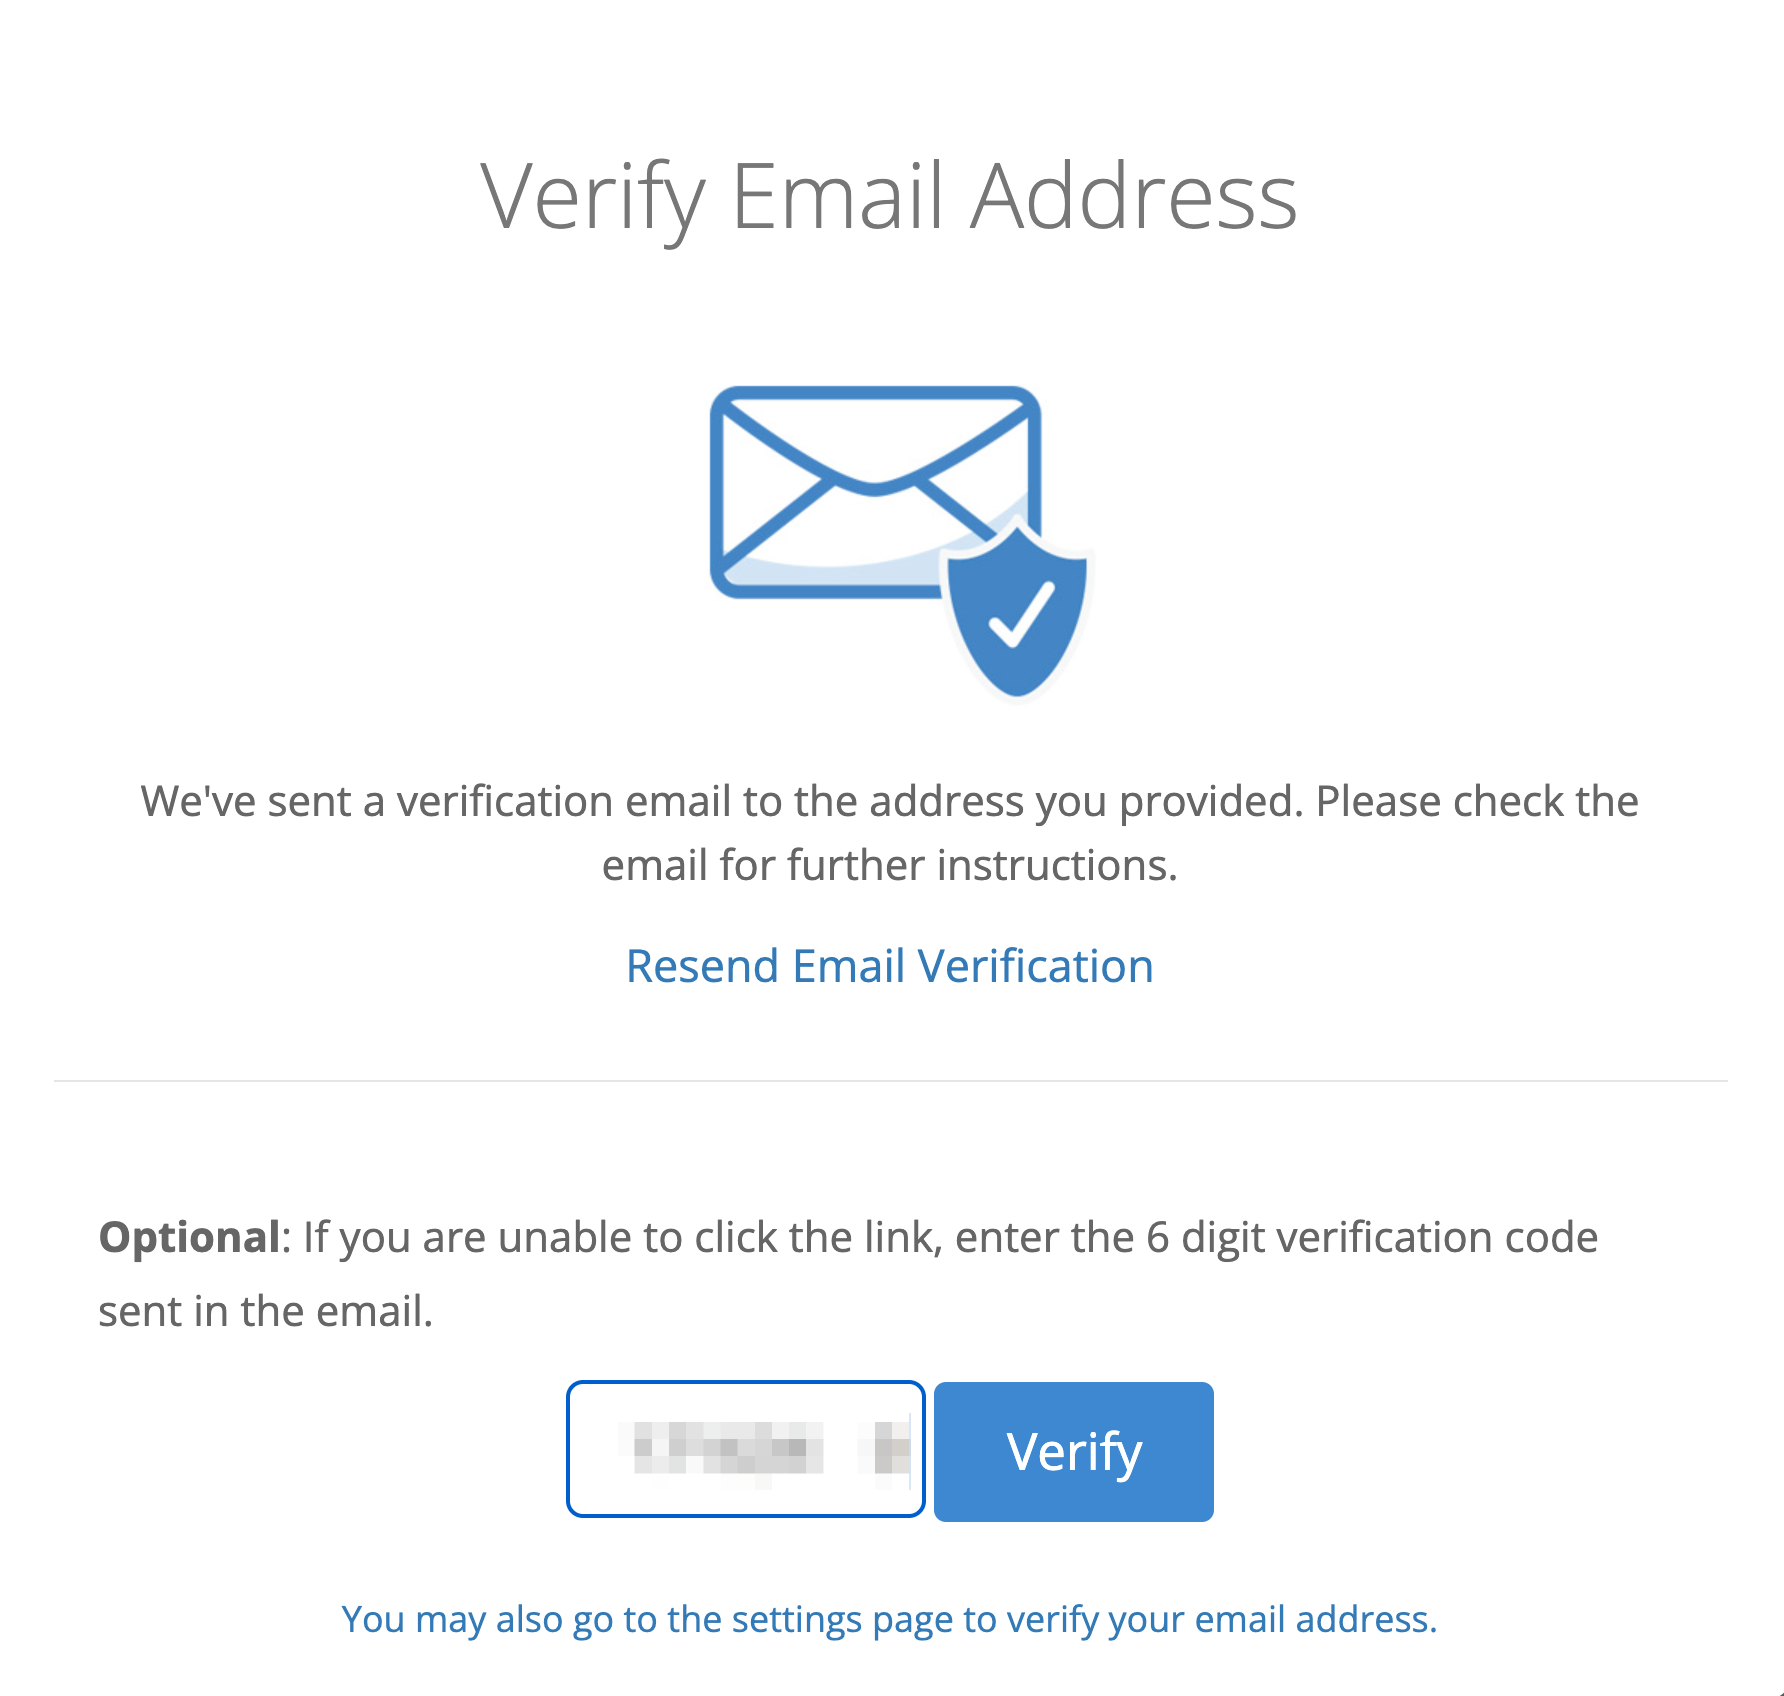
You will receive a verification email. When you do, enter the code provided.
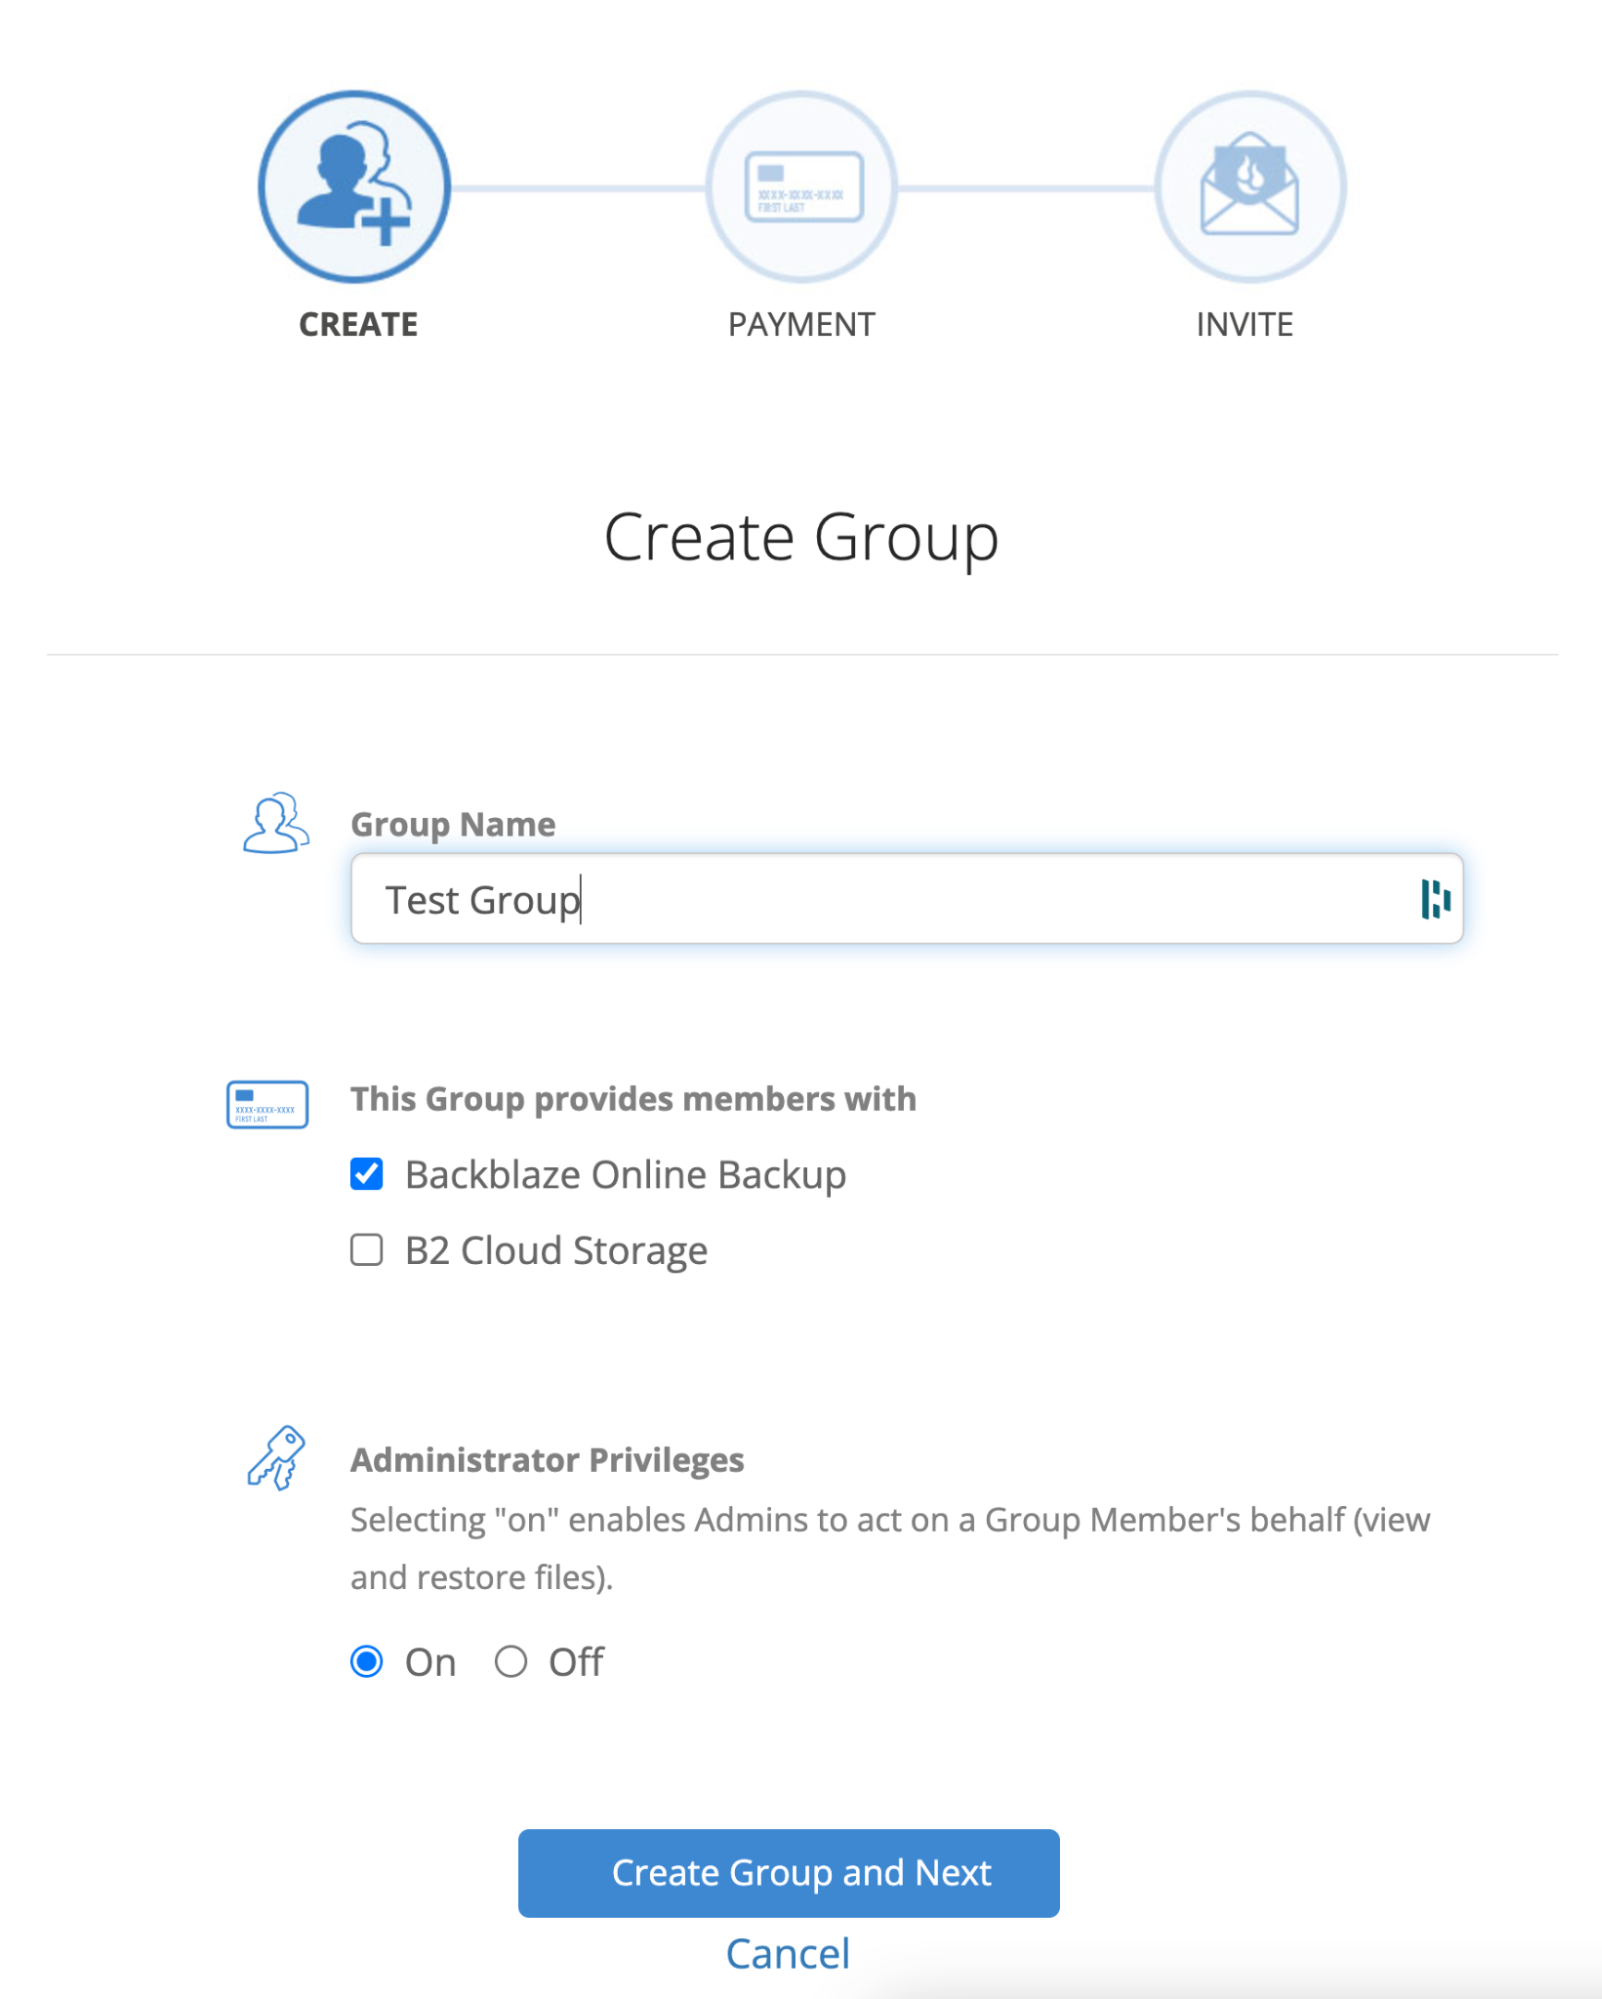
Now, create a Group for your users. There are a few reason to create a group or groups for your users, including:
To establish separate retention periods.
To use different billing methods for different groups.
To give different kinds of users customized access.
To keep your users organized according to your needs.
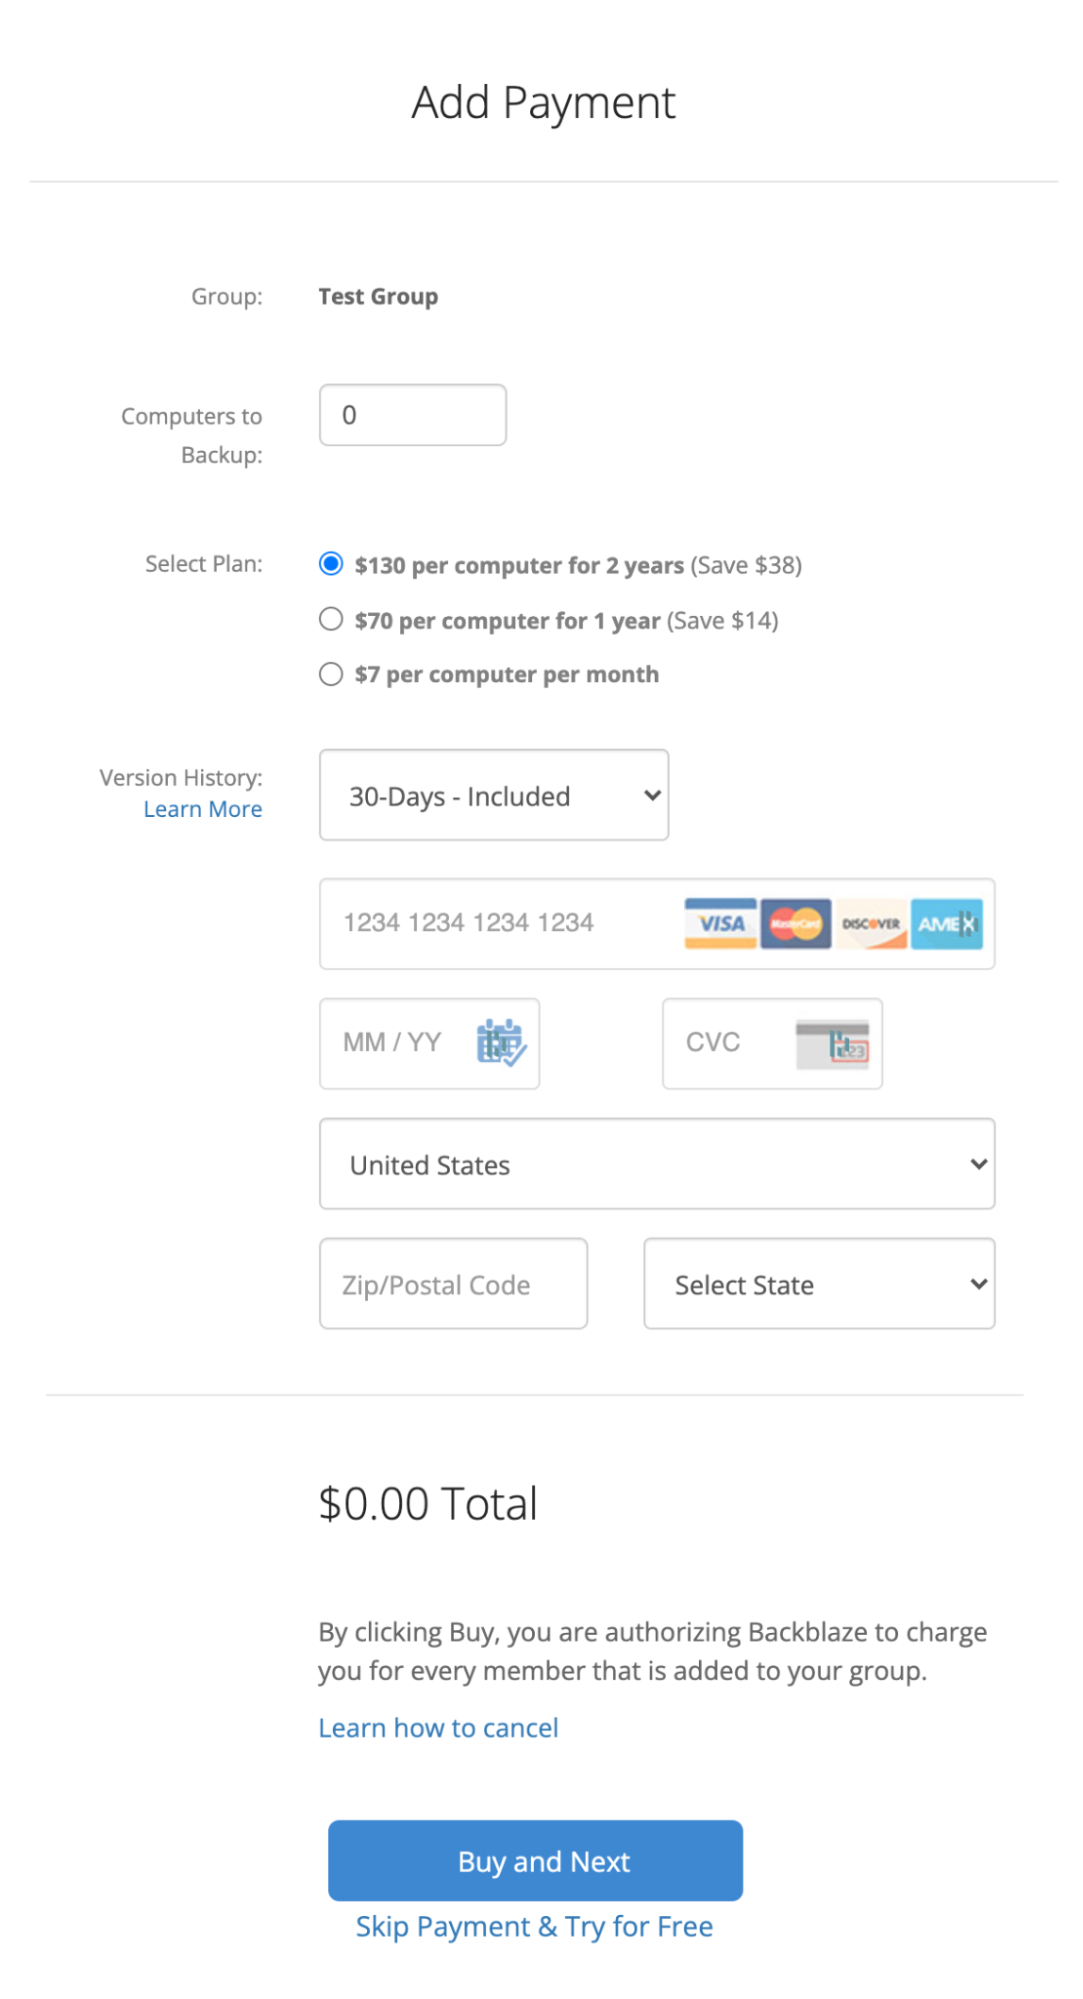
Choose how many licenses you would like to purchase in the Computers to Backup field, select your retention plan under Version History, then click Add a Billing Method and enter your information. When you are done, click Buy and Next (If you are not ready to proceed with adding a payment method, feel free to click “Skip Payment & Try for Free”, this will allow you to try out the product for 15 days with full functionality.)
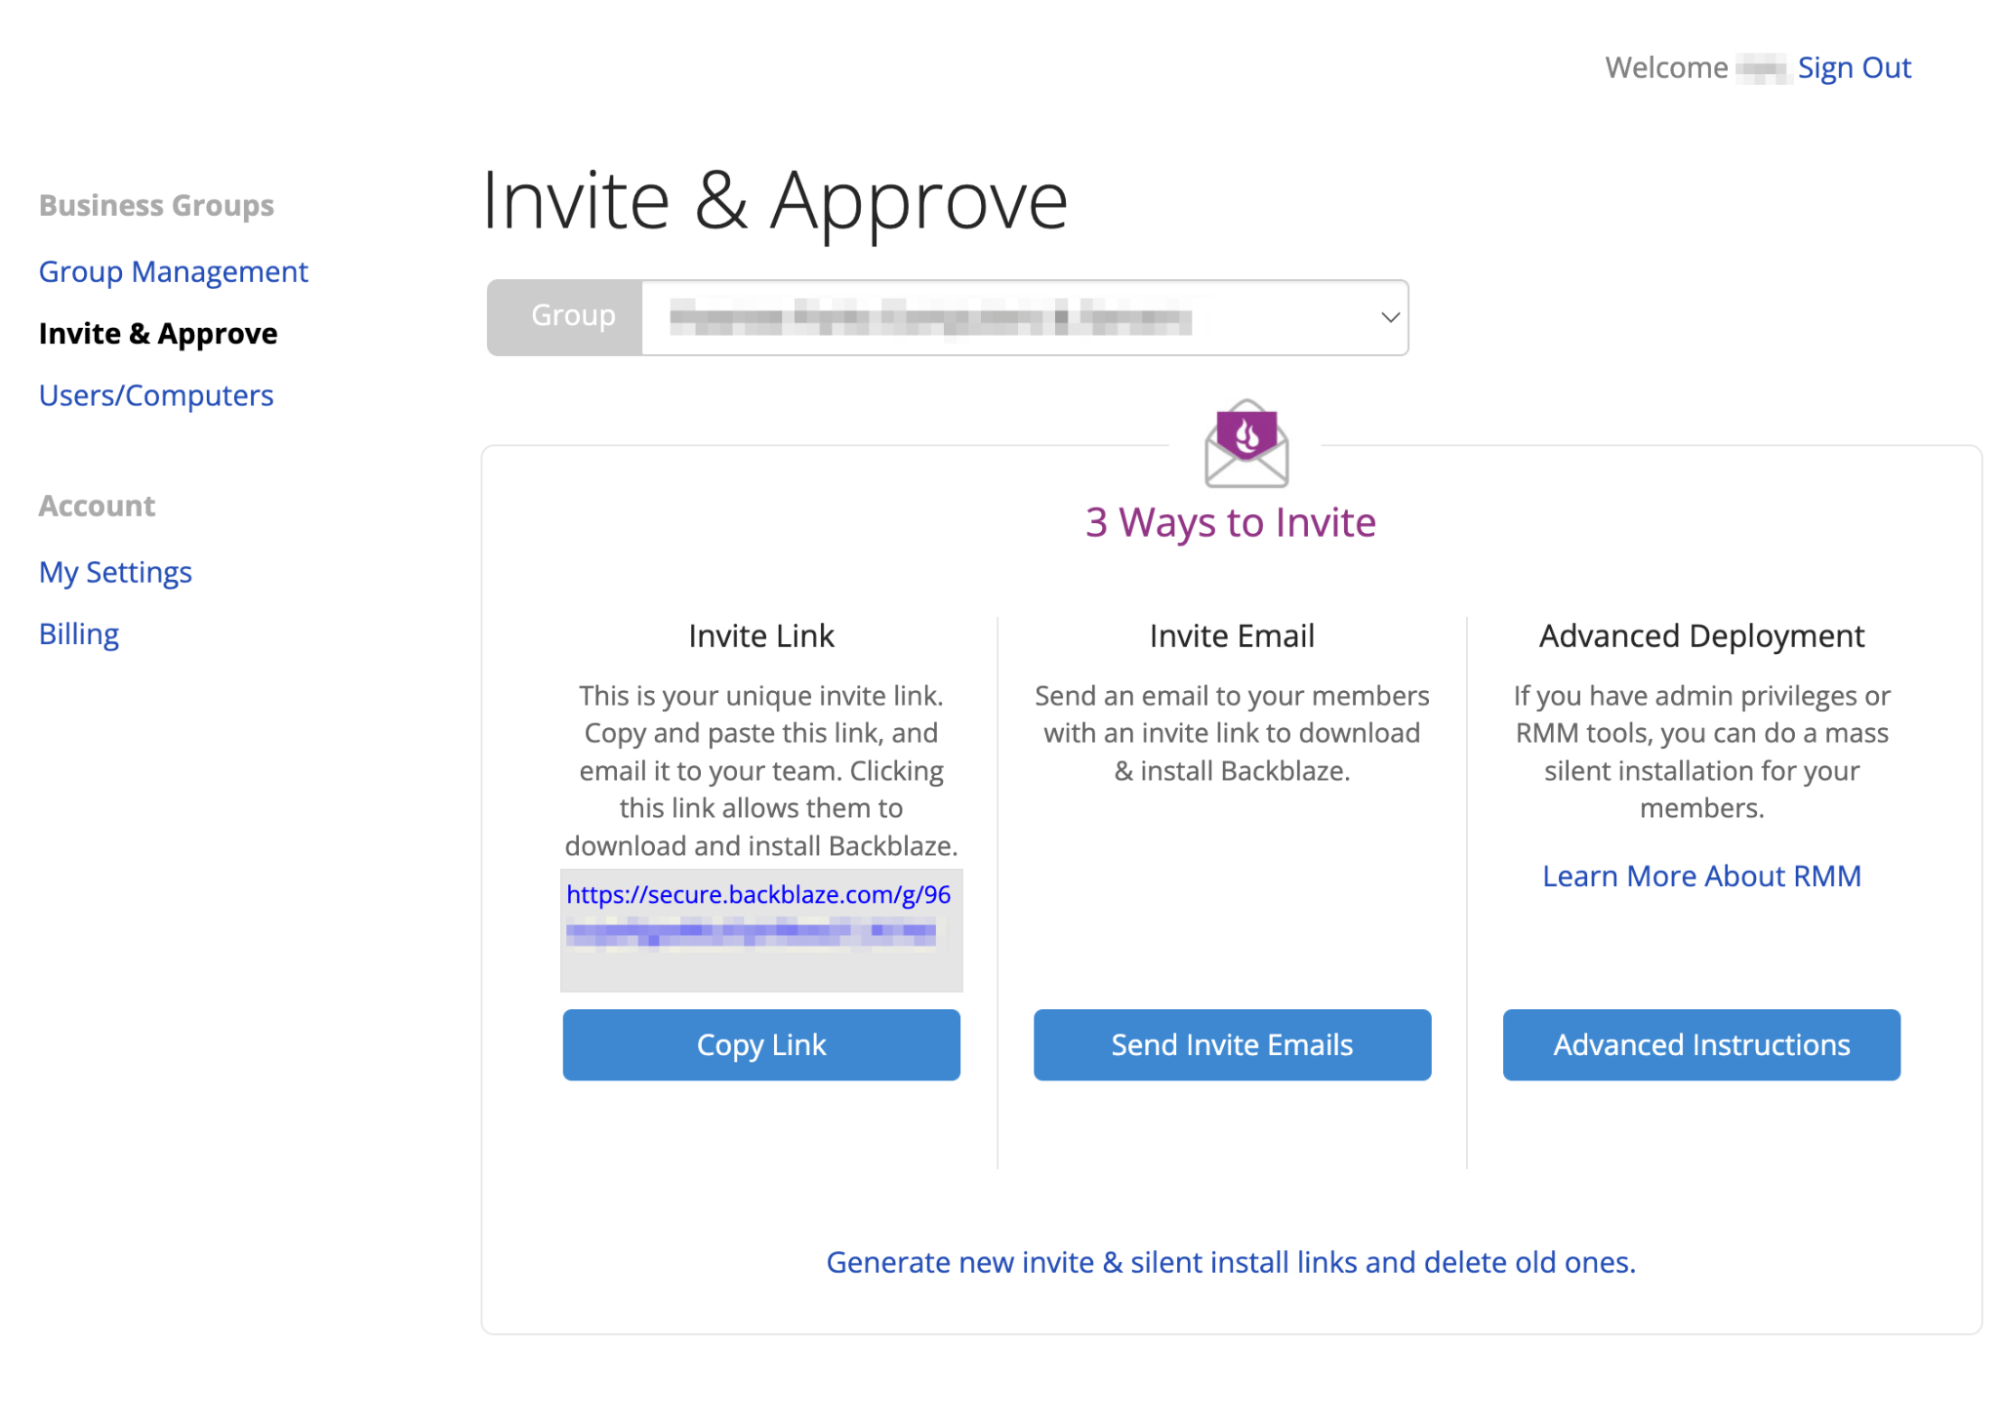
Now that your Group is created, you have some options on how to invite users into the group. You can:
Backblaze offers a number of different deployment options to give you the most flexibility when deciding how to deploy the Backblaze client to your machines. It can be as simple as sending the invite link via Slack or in a personally crafted email to a handful of users. You can use our Invite Email option to just add email addresses to a canned invite. Or you can deploy via a silent install using RMM tools such as JAMF, SCCM, Munki and others to deploy the software to your end users. Assistance is always available from our solution engineers to help guide you through the deployment process.
Additional Configuration Considerations
With Backblaze Business Backup, you can customize your groups’ administrative access. Specify who has administrator privileges to a group simply by adding an email address to the group settings. As a group administrator, you have the ability to assist your users with restores and be aware of issues when they arise.
You can also integrate with your Single Sign-on provider—either Google or Microsoft—in the settings to improve security, reduce support calls, and free users from having to remember yet another password.
An Invitation to Try Backblaze
If you are a CrashPlan user looking to transition to a new cloud backup service for your workstations, Backblaze makes moving to the cloud easy. Reach out to us at any time for help transitioning and getting started.
A lot has happened since we published our last Ransomware Takeaways, and it’s only been three months. High-profile attacks dominated headlines last quarter, but the attacks few of us ever hear about made up the majority, often with more serious consequences than higher gas prices. In a recent survey of 130 hospitals and healthcare organizations, nearly half of them reported they had to disconnect their networks in the first half of 2021 due to ransomware.
You surely follow ransomware news if you have any responsibility for your organization’s IT infrastructure and/or data. Still, since the dynamics are ever changing, you might find it useful to see the bigger picture developments as we’re seeing them, to help inform your decision making. Here are five quick, timely, shareable takeaways from our monitoring over Q2 2021.
This post is a part of our ongoing series on ransomware. Take a look at our other posts for more information on how businesses can defend themselves against a ransomware attack, and more.
The REvil ransomware syndicate started negotiations at $70 million in an attack on Kaseya that affected 1,500 businesses that use the company’s software products. The $70 million demand follows on the heels of two $50 million demands by REvil against computer manufacturer, Acer, in March and Apple supplier, Quanta, in April.
While the highest demands reach astronomical heights, average demands are also increasing according to cybersecurity and cyber insurance firm, Coalition. In their H1 2021 Cyber Insurance Claims Report, they noted the average ransom demand made against their policyholders increased to $1.2 million per claim in the first half of 2021, up from $450,000 in the first half of 2020.
2. Ransom Payments Appeared to Fluctuate
In their 2021 Ransomware Threat Report, Cybersecurity firm, Palo Alto Networks, noted an 82% increase in average ransom payments in the first half of 2021 to a record $570,000. While cybersecurity firm, Coveware, which tracks payments quarterly, reported a lower figure—in Q2 of 2021, they put average payments at $136,576 after hitting a high of $233,817 in Q4 of 2020. The different sources show different trends because tracking payments is a tricky science—companies are not required to report incidents, let alone ransoms demanded or payments made. As such, firms that track individual payments are limited by the constituencies they serve and the data they’re able to gather.
Taking a different approach, Chainalysis, a blockchain data platform that tracks payments to blockchain addresses linked to ransomware attacks, showed that the total amount paid by ransomware victims increased by 311% in 2020 to reach nearly $350 million worth of cryptocurrency. In May 2021, they published an update after identifying new addresses that put the number over $406 million. They expect the number will only continue to grow.
We’ll continue to track reporting from around the industry and account for variances in future reporting, but the data does tell us one thing—ransomware continues to proliferate because it continues to be profitable.
3. Double Extortion Tactics Are Increasing
In addition to encrypting files, cybercriminals are stealing data with threats to leak it if companies don’t pay the ransom. This trend is particularly concerning for public sector organizations and companies that maintain sensitive data like the Washington, D.C. Metropolitan Police Department—the victim of a May 2021 attack by the Babuk group that leaked sensitive documents including staff disciplinary records and security reports from the FBI and CIA.
Double extortion is not new—the Maze ransomware group carried out the first extortion attack in 2019, but the tactic is becoming more prevalent. In their Threat Report, Palo Alto Networks found that at least 16 ransomware variants currently employ this approach, and they expect more ransomware brands to adopt the tactic.
4. Ransomware Syndicates Are in Flux
The limelight is not a place most ransomware syndicates want to be. We’ve seen reports that the DarkSide group, responsible for the Colonial Pipeline attack, seems to have dissolved under the increased attention. But, the ransomware economy is porous, and different sources report that the muscle behind the gang may simply have changed horses to a new brand—BlackMatter—or a simply a different one—LockBit, the group allegedly responsible for the reported attack on Accenture. Like a high-stakes game of whack-a-mole, ransomware brands and groups are continuing to morph and change as authorities get wise to their tactics.
5. SMBs Continue to Be Main Targets, and Healthcare Suffered Doubly
Cybercriminals target organizations of this size because they know they’re vulnerable. Small and medium-sized businesses (SMBs) with strapped IT budgets are less likely to have the resources to protect themselves and more likely to pay the ransom rather than suffer extended downtime trying to recover from an attack.
While hospitals struggled to respond to the global COVID-19 pandemic, they also suffered cybersecurity breaches at an alarming rate. As noted above, almost half of 130 hospitals surveyed in a new study reported that they disconnected their networks in the first half of 2021 due to ransomware. Some did so as a precautionary measure while others were forced to do so by the severity of the ransomware infection. Medium-sized hospitals with less than 1,000 beds experienced longer downtime and higher losses than larger institutions, averaging almost 10 hours of downtime at a cost $45,700 per hour. As we reported in our last quarterly update, relying on the goodwill of cybercriminals to forgo attacks on organizations that serve the public good is a mistake.
The Good News
This quarter, the good news is that the increased attention means ransomware groups are under more scrutiny and more businesses are waking up to the reality that the threat is very, very real. Fortunately, the headlines and numbers make it even easier to justify the investment in ransomware protections, and there are plenty of ways to incorporate them into your cloud infrastructure. If your IT team does one thing in 2021, making ransomware resilience a priority should be it.
What You Can Do to Defend Against Ransomware
For more information on the threat SMBs are facing from ransomware and steps you can take to protect your business, read our Complete Guide to Ransomware.
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.