Tag Archives: Emerging Threats

CVE-2026-85706: Critical GitLab Path Traversal Exploited in the Wild

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/etr-cve-2026-85706-critical-gitlab-path-traversal-exploited-in-the-wild

Overview

On September 10, 2026, GitLab published a critical patch release for GitLab Community Edition (CE) and Enterprise Edition (EE). The release addresses CVE-2026-85706, a critical path traversal vulnerability (CWE-22) in the repository commits API with a CVSSv3.1 score of 10.0. According to GitLab, improper path confinement and missing authentication enforcement could allow an unauthenticated user to read arbitrary files from an affected GitLab server under certain conditions.

On September 11, 2026, CVE-2026-85706 was added to the U.S. Cybersecurity and Infrastructure Security Agency’s (CISA) Known Exploited Vulnerabilities (KEV) catalog, based on evidence of active exploitation. CISA set a remediation due date of September 14, 2026, for affected Federal Civilian Executive Branch agencies and marked the vulnerability as subject to forensic triage requirements under Binding Operational Directive 26-04.

Organizations running affected self-managed GitLab instances should remediate CVE-2026-85706 on an emergency basis, outside of normal patch cycles.

Mitigation guidance

A vendor-supplied update is available to remediate CVE-2026-85706. Organizations running affected self-managed GitLab CE or EE instances should upgrade to a fixed version immediately.

Affected GitLab CE/EE versions

Fixed version

All versions from 18.7 before 19.1.8

19.1.8

All versions from 19.2 before 19.2.6

19.2.6

All versions from 19.3 before 19.3.2

19.3.2

GitLab.com is already running a patched version, and GitLab Dedicated customers do not need to take action. Per GitLab, all self-managed deployment types are affected, including Omnibus, source code, and Helm chart deployments.

The updates include database migrations. Single-node installations will experience downtime while the migrations run; multi-node deployments can use GitLab’s zero-downtime upgrade procedure. Of the fixed releases, only 19.3.2 includes post-deployment migrations.

The patch release also addresses 17 other vulnerabilities. These include CVE-2026-87719, a critical insecure deserialization vulnerability (CWE-502) in GitLab EE with a CVSSv3.1 score of 9.9. GitLab states that, under certain conditions, an authenticated user with Duo Chat access could obtain Advanced Search instance configurations and sensitive credentials using a specially crafted GraphQL subscription argument. At the time of publication, only CVE-2026-85706 is known to be exploited in the wild.

Given the confirmed exploitation, Rapid7 strongly recommends looking for signs of compromise even after the update has been applied. Organizations subject to CISA’s BOD 26-04 should also follow the forensic triage requirements associated with the KEV entry.

For the latest mitigation guidance, please refer to the vendor’s security advisory.

Rapid7 customers

Exposure Command, InsightVM, and Nexpose

Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-85706 with a vulnerability check available in the September 15 content release.

Updates

  • September 14, 2026: Initial publication.

CVE-2026-63030: wp2shell a Critical Remote Code Execution Vulnerability in WordPress Core

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/etr-cve-2026-63030-wp2shell-a-critical-remote-code-execution-vulnerability-in-wordpress-core

Overview

On July 17, 2026, a GitHub Security Advisory was published for CVE-2026-63030, a critical unauthenticated remote code execution vulnerability affecting WordPress Core. WordPress Core. While the official GitHub security advisory classifies the severity as Critical, the vulnerability has currently been assigned a CVSS score of 7.5. WordPress is one of the most widely deployed content management systems, making vulnerabilities in its core software potentially significant for organizations operating public-facing websites. The vulnerability reportedly allows an unauthenticated attacker to execute code via the WordPress REST API batch endpoint, potentially resulting in complete compromise of the website and its underlying data. No valid account or user interaction is required.

According to the advisory, the vulnerability affects WordPress versions 6.9.0 through 6.9.4 and versions 7.0.0 through 7.0.1. The issue is fixed in WordPress 6.9.5 and 7.0.2. A fix is also included in WordPress 7.1 Beta 2.

Cloudflare reported that the vulnerable code path can be reached when a persistent object cache is not in use. Searchlight Cyber, whose researchers identified the vulnerability, stated that it can be exploited remotely against a default WordPress installation without requiring additional plugins.

Technical exploit details have not yet been published by Searchlight Cyber, as of July 17 5:45 PM Eastern time. At the time of publication, Rapid7 is not aware of publicly confirmed in-the-wild exploitation. Organizations should not interpret the absence of public exploitation reports as an indication of low risk, particularly given the vulnerability’s unauthenticated attack path and the widespread deployment of WordPress; affected WordPress sites should be urgently patched.  Due to WordPress Core being an open-source project and given the current ability of AI models to analyze open-source code, Rapid7 Labs believes it is highly likely that a public PoC will be made available in a short period of time.

Mitigation guidance

Organizations operating affected WordPress installations should prioritize upgrading immediately. Applying the WordPress-provided update is the most effective way to remediate CVE-2026-63030.

Affected and fixed versions include:

WordPress branch

Affected versions

Fixed version

Earlier than 6.9

Not affected by CVE-2026-63030

No action required for this CVE

6.9

6.9.0 through 6.9.4

6.9.5

7.0

7.0.0 through 7.0.1

7.0.2

7.1 beta

Affected beta versions were not fully specified

7.1 Beta 2

WordPress maintainers stated they are forcing updates for affected installations with automatic updates enabled. Administrators should nevertheless verify that each internet-facing WordPress website has successfully upgraded to WordPress 6.9.5, 7.0.2, or another fixed release appropriate for its branch. Workarounds are not recommended at this time.

Rapid7 customers

Exposure Command, InsightVM, and Nexpose

Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-63030 with authenticated vulnerability checks available in the July 20th, 2026 content release.

Updates

July 17, 2026: Initial publication.

CVE-2026-55040: Microsoft SharePoint JWT Token Authentication Bypass (FIXED)

Post Syndicated from Stephen Fewer original https://www.rapid7.com/blog/post/ve-cve-2026-55040-microsoft-sharepoint-jwt-token-authentication-bypass-fixed

Overview

Rapid7 Labs conducted a zero-day research project against Microsoft SharePoint, resulting in the discovery of two new vulnerabilities that, when chained together, achieve unauthenticated remote code execution (RCE) against a vulnerable SharePoint server. Today, both Rapid7 and Microsoft are disclosing the first vulnerability in this chain, the authentication bypass vulnerability CVE-2026-55040. The RCE component of the exploit chain is expected to be patched by Microsoft in the next update cycle for August 2026. The exploit chain was developed as an entry for the recent Pwn2Own Berlin hacking competition – part of Rapid7 Labs’ continued effort to raise the bar in Vulnerability Intelligence and our commitment to the preemptive protection of our customers through original vulnerability research.

A remote unauthenticated attacker can leverage CVE-2026-55040 to bypass authentication on a vulnerable SharePoint server and perform operations as a SharePoint site user or administrator. The vulnerability is due to several issues in the JWT token validation pipeline.

CVE-2026-55040 has a CVSSv3.1 score of 5.3 (Medium), and a Common Weakness Enumeration (CWE) of CWE-1390: Weak Authentication.

Product description

Microsoft SharePoint is a ubiquitous, web-based collaboration and document management platform deeply integrated into the Microsoft 365 ecosystem. Serving as the central hub for corporate intranets, internal file sharing, and workflow automation, it is trusted by enterprises worldwide to store and manage vast repositories of sensitive business data. Because SharePoint acts as a critical bridge between internal users, active directories, and cloud infrastructure, vulnerabilities within its architecture present a high-risk attack surface.

Impact

By leveraging CVE-2026-55040, a remote unauthenticated attacker can assume the identity of any SharePoint site user; the prerequisite is the attacker must know in advance the user they wish to identify as. This can be achieved in a number of ways, including via a user’s Active Directory (AD) Security ID (SID), or via a user’s AD User Principal Name (UPN). A UPN is the primary logon name for a user in either Windows AD or Microsoft Entra ID, and is formatted similar to that of an email address, e.g. [email protected].

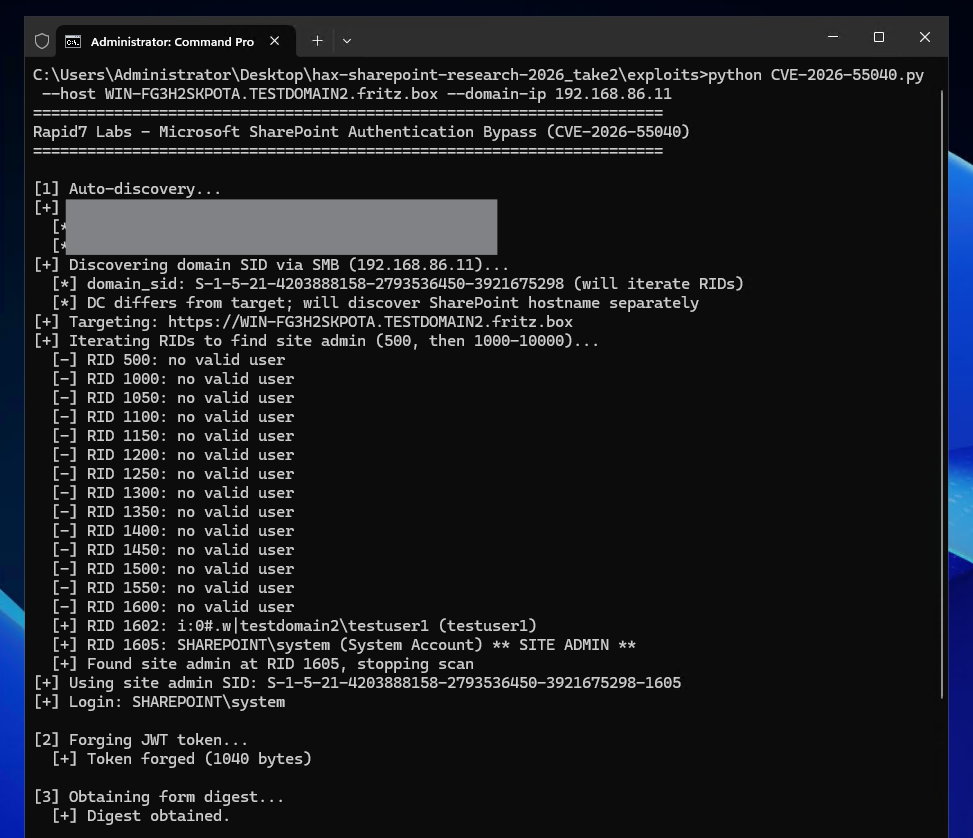
In the example screenshot below, with identifying information redacted, a Rapid7 Labs proof-of-concept script discovers potential SharePoint users via SID enumeration and then leverages CVE-2026-55040 to bypass authentication on the target SharePoint site to assume the identity of that user — ultimately identifying the SharePoint site administrator user account.

Rapid7-Labs-PoC-CVE-2026-55040.png
Figure 1: The Rapid7 Labs PoC for CVE-2026-55040.

An attacker who successfully exploits CVE-2026-55040 can perform operations against the target SharePoint site as the user they identify as. Furthermore, this authentication bypass can be chained to additional vulnerabilities within the authenticated attack surface of the target site.

Rapid7 Labs has chained the authentication bypass CVE-2026-55040 with a separate RCE vulnerability for unauthenticated RCE. Patching CVE-2026-55040 will successfully break this exploit chain. The RCE component has been disclosed to Microsoft and is expected to be patched in the scheduled August patch cycle. The chaining of vulnerabilities highlights that even though the authentication bypass has been assigned a medium severity CVSS score by Microsoft, the impact of successfully chaining a medium severity authentication bypass to an RCE component is significant. This also underscores the importance of patching vulnerabilities such as authentication bypasses, which can break complex and high impact exploit chains.

Leveraging AI

To develop our SharePoint exploit chain, Rapid7 Labs undertook a research project divided into two main sprints, the first in January and the second in March, 2026. While both sprints did encompass more traditional vulnerability research such as manual code review and reverse engineering, a significant amount of the work was undertaken through an agent. Over 24 active days of agentic work, we leveraged 96 sessions, issued 256 prompts, and generated approximately 80,000 agentic tool calls.

The initial January sprint was unsuccessful, resulting in no findings that could be leveraged for an exploit chain. We used this sprint to experiment with several different publicly available models, along with different workflows to navigate and reason across a massive and complex codebase. However, our second sprint in March was successful and yielded, through a heavily prompted agent, a two-vulnerability exploit chain that achieved unauthenticated RCE.

The improvement in quality between January and March in terms of agentic work, along with our improved workflows, was noticeable. This highlights the speed at which this field is evolving, how publicly available models are improving, and how as research teams develop their workflows, the results begin to compound.

Credit

This vulnerability was discovered by Stephen Fewer, Senior Principal Security Researcher at Rapid7 and is being disclosed in accordance with Rapid7’s vulnerability disclosure policy.

Vendor statement

The following statement has been provided by Microsoft:

“We would like to thank Rapid7 for responsibly reporting this issue through coordinated vulnerability disclosure.”

Technical analysis

Rapid7 will be publishing full technical details for CVE-2026-55040 within 30 days of this disclosure.

Remediation

Customers are advised to apply the latest available updates for the impacted product to ensure they are protected.

Rapid7 customers

Exposure Command, InsightVM and Nexpose customers will be able to assess their exposure to CVE-2026-55040 with Authenticated vulnerability checks available in the July 14 content release

Disclosure timeline

  • May 18, 2026: Rapid7 discloses an unauthenticated RCE exploit chain to Microsoft. Microsoft acknowledges receipt of the disclosure the same day.

  • May 20, 2026: Microsoft confirms the findings and indicates that the exploit chain will be patched across two scheduled update cycles – the authentication bypass component in July, and the RCE component in August.

  • May 21, 2026: Rapid7 acknowledges the disclosure schedule and requests supporting information. Microsoft requests a 30 day stay on disclosure of technical details and publication of PoC.

  • May 29, 2026: Rapid7 agrees to a 30 day stay on technical details with a proviso to publish earlier should either exploitation in-the-wild or third-party publication of details occur within the 30 days. Microsoft confirms the disclosure plan the same day.

  • June 30, 2026: Rapid7 requests supporting information for the upcoming disclosure.

  • June 30, 2026: Microsoft provides supporting information to Rapid7.

  • July 14, 2026: This disclosure for CVE-2026-55040.

CVE-2026-41940: cPanel & WHM Authentication Bypass

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/etr-cve-2026-41940-cpanel-whm-authentication-bypass

Overview

On April 28, 2026, cPanel issued a security update to fix a critical vulnerability affecting the cPanel & WHM and WP Squared products. In the cPanel release notes, the bug was described as “an issue with session loading and saving.” CVE-2026-41940, the identifier subsequently assigned on April 29, 2026, has a CVSS score of 9.8 and allows unauthenticated remote attackers to bypass authentication and gain unauthorized administrative access to the affected systems. First-party cPanel & WHM and WP Squared vendor advisories are available.

cPanel & WHM is web hosting control panel software used to manage websites and servers. WHM provides root-level administration, while cPanel acts as the user-facing interface. Successful exploitation of CVE-2026-41940 grants an attacker control over the cPanel host system, its configurations and databases, and websites it manages. A naive Shodan query for potential targets returns approximately 1.5 million cPanel instances exposed to the internet that may be vulnerable.

A managed cPanel host, KnownHost, stated that CVE-2026-41940 is actively being exploited in the wild, with speculation of targeted zero-day exploitation happening as early as February 23, 2026, prior to the vulnerability’s public disclosure. Security firm watchTowr has published a technical analysis and proof-of-concept exploit for CVE-2026-41940. As such, widespread exploitation in the wild is expected to be imminent.

Technical overview

Systems exposing the affected web service software are vulnerable by default.

As of April 29, 2026, a technical analysis and proof-of-concept exploit have been published by security firm watchTowr. CVE-2026-41940 is an authentication bypass caused by a Carriage Return Line Feed (CRLF) injection in the login and session loading processes of cPanel & WHM.

Before authentication occurs, `cpsrvd` (the cPanel service daemon) writes a new session file to the disk. The vulnerability allows an attacker to manipulate the `whostmgrsession` cookie by omitting an expected segment of the cookie value, avoiding the encryption process typically applied to an attacker-provided value. Attackers can inject raw `\r\n` characters via a malicious basic authorization header, and the system subsequently writes the session file without sanitizing the data. As a result, the attacker can insert arbitrary properties, such as `user=root`, into their session file. After triggering a reload of the session from the file, the attacker establishes administrator-level access for their token.

Mitigation guidance

Organizations running on-premise instances of cPanel & WHM or WP Squared should prioritize upgrading to a fixed version on an emergency basis. Some hosting providers have opted to temporarily institute workaround TCP port blocks for cPanel & WHM web services on ports 2083 and 2087. However, defenders are strongly advised to patch, rather than implement workarounds.

Affected Software:

  • cPanel & WHM 11.110.0 versions prior to fixed version 11.110.0.97

  • cPanel & WHM 11.118.0 versions prior to fixed version 11.118.0.63

  • cPanel & WHM 11.126.0 versions prior to fixed version 11.126.0.54

  • cPanel & WHM 11.132.0 versions prior to fixed version 11.132.0.29

  • cPanel & WHM 11.134.0 versions prior to fixed version 11.134.0.20

  • cPanel & WHM 11.136.0 versions prior to fixed version 11.136.0.5

  • WP Squared 11.136.1 versions prior to fixed version 11.136.1.7

Please read the vendor advisory for the latest guidance.

Exposure Command, InsightVM, and Nexpose

Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-41940 with authenticated vulnerability checks expected to be available in the April 30, 2026 content release.

Updates

April 29, 2026: Initial publication.

CVE-2026-33032: Nginx UI Missing MCP Authentication

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/etr-cve-2026-33032-nginx-ui-missing-mcp-authentication

Overview

On March 30, 2026, a security advisory was published for a critical vulnerability affecting Nginx UI. Nginx UI is an open-source web interface to centralize the management of Nginx configurations and SSL certificates. The critical vulnerability, CVE-2026-33032, was reported in early March by Pluto Security researcher Yotam Perkal and subsequently patched on March 15, 2026. That same day, Pluto Security published a technical blog post with some vulnerability details.

CVE-2026-33032 is a missing authentication bug with a CVSS score of 9.8; as a result of missing authentication controls, an unauthenticated attacker can access a Model Context Protocol (MCP) server that can perform privileged operations on managed Nginx web servers. Systems are vulnerable in the default IP allowlist configuration, which allows any remote IP to access MCP functionality. Exploitation results in full attacker control of the managed Nginx service. 

According to a Recorded Future report published on April 13, 2026, exploitation of CVE-2026-33032 in the wild has begun.

Mitigation guidance

Organizations running Nginx UI should prioritize updating on an urgent basis to remediate CVE-2026-33032. Additionally, to reduce exposure to future vulnerabilities affecting Nginx UI, defenders should ensure that network access to the Nginx UI management interface is strictly limited to those who must have it.

Affected versions:

According to the finder’s blog post, version 2.3.3 and prior are affected, and the fix is present in version 2.3.4 and later. However the official CVE record states that versions 2.3.5 and below are affected. This discrepancy in affected version numbers makes it unclear as to the correct version required to remediate CVE-2026-33032. To avoid this version number discrepancy, users are advised to update to the very latest version (2.3.6).

Please read the vendor advisory for the latest guidance.

Rapid7 customers

Exposure Command, InsightVM, and Nexpose

Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-33032 with unauthenticated checks expected to be available in the April 17 content release.

Updates

  • April 16, 2026: Initial publication.

FortiGate CVE-2025-59718 Exploitation: Incident Response Findings

Post Syndicated from Eric Carey original https://www.rapid7.com/blog/post/ve-fortigate-cve-2025-59718-exploitation-incident-response-ir-findings

Rapid7’s Incident Response (IR) team was engaged to investigate an incident involving exploitation of CVE-2025-59718 against a vulnerable FortiGate appliance. In December 2025, Fortinet disclosed this improper verification of cryptographic signature vulnerability that facilitates an SSO login bypass on affected appliances. After the initial exploitation, the attackers maintained a low-profile posture, systematically compromising additional firewalls before moving to internal network hosts. Ultimately, this grace period allowed responders to contain the threat before further impact could occur within the environment. This blog details exploitation insights, attack progression, and practical detection opportunities for defenders handling their own environments.

Investigative methodology: Tracing the initial access vector in FortiGate appliances

Identifying the Initial Access Vector (IAV) is a cornerstone of any incident response engagement. However, when the source of compromise is not immediately obvious, particularly when edge device exploitation is involved, responders often need to take a broader investigative approach. Rather than starting with a clear point of entry, investigators must analyze the available telemetry, reconstruct attacker activity, and work backwards to determine how access was first obtained.

This process often involves multiple investigative workstreams running in parallel, each designed to answer different questions about the intrusion. As many IR responders and enthusiasts know, the first suspicious event observed during an investigation is rarely the first action taken by the attacker. Instead, it typically represents a point somewhere in the middle of a larger attack chain.

A key step in incident response investigations is reconstructing the attacker timeline. Responders often take an “inside out” approach where they move outward from the initial alert to the full scope of the malicious activity (IAV), correlating multiple data sources to map the unfolding of the event. This process involves examining authentication logs, endpoint telemetry, firewall events, and records of system changes, rather than depending on just one log source. It also typically requires frequent pivoting between artifacts as investigations rarely ever unfold in a linear fashion. By aligning these findings and events chronologically, investigators often identify activity that predates the initial alert.

CVE-2025-59718: Technical analysis and observed attacker behavior

The first activity that drew attention was enumeration and credential discovery within the internal environment. This basic enumeration included gathering information about users, systems, and accessible resources within common user directories. This activity eventually expanded to SMB-based file scraping and network share access, allowing attackers to review files stored across the environment. While this behavior resembled routine administration, the chronological sequence of file scraping and network share access painted a clear picture of an attacker’s initial discovery phase.

Digging deeper into the credential discovery activity, the popular tool Mimikatz was utilized to harvest credentials from various sources within the impacted environment. The attacker’s objective was to obtain valid credentials to an elevated admin account with the goal to blend in.

With credentials in hand and mimicking admin activity to disguise their actions, the attacker was then enabled to move laterally throughout the environment using common administrative tools and access methods. PsExec and Microsoft Remote Desktop (RDP) were two tools utilized for lateral movement while standard web browsers facilitated application access.

Attackers appeared particularly interested in systems that could provide broader access to the environment, including virtualization platforms, domain controllers, and servers supporting backup infrastructure. These systems often represent high-value targets for attackers seeking to escalate privileges, access sensitive data, or disrupt recovery capabilities.

Responders were working simultaneously to contain the attacker while building the narrative to cut them off at the source. With the current understanding of the narrative, the IAV puzzle began to unravel as more information came to light. Strangely, the first authentication into the Windows environment originated from an internal IP address that did not align with the known internal IP address ranges. It turns out, this internal IP address fell within the DHCP lease range of the FortiGate device. At first glance, this could be written off as legitimate VPN activity. However, to create even more questions, it was revealed that the FortiGate SSL VPN was never turned on within this environment. This revelation made the FortiGate device a prime suspect for IAV.

Taking a closer look at the FortiGate device, specifically system logs and configuration data, revealed early indications that the device had been modified to support continued access. The SSL VPN component had been enabled, and multiple configuration changes were identified, including edits to VPN settings, the creation of new firewall policies, and adjustments to configuration parameters. These changes appeared in FortiGate system logs as configuration updates similar to the following:

logid="0100044546" type="event" subtype="system" level="information"
vd="root" logdesc="Attribute configured" user="admins"
ui="GUI(45.32.216[.]250)" action="Edit" cfgpath="vpn.ssl.settings"
msg="Edit vpn.ssl.settings"

logid="0100044547" type="event" subtype="system" level="information" 
vd="root" logdesc="Object attribute configured" user="admins" 
ui="GUI(45.32.216[.]250)" action="Add" cfgpath="firewall.policy" 
cfgobj="XX" msg="Add firewall.policy <redacted>"

While these types of changes may seem routine in isolation, it is the combination and timing of these actions that raises concerns from a responder’s perspective. The investigation’s next key clue was identified when the source of these changes was traced back to a newly created account.

Following this thread further, investigators identified that multiple accounts had been created on the device, including SSO administrator, system administrator, and local accounts. Several of these accounts were associated with email domains attributed to Namecheap-hosted infrastructure, including domains such as openmail[.]pro. Notably, some of the newly created SSO administrator accounts were linked to forticloud.com domains as reflected in log entries such as:

Object attribute configured(Add system.sso-forticloud-admin <attacker account>@forticloud.com-1)

For responders, the creation of multiple new administrative accounts is often a strong indicator of persistence being established. Continuing to work backwards through the timeline, investigators identified that prior to these account creation events, the device’s configuration file was downloaded through the FortiGate UI. From an investigative perspective, configuration exports are highly valuable to attackers because they effectively serve as a blueprint of the environment, exposing network architecture, authentication mechanisms/settings, device relationships, and occasionally, sensitive credentials.

logid="0100032095" type="event" subtype="system" level="warning" 
vd="root" logdesc="Admin performed an action from GUI" user="admin" 
ui="GUI(104.28.227[.]105)" action="download" status="success" 
msg="System config file has been downloaded by user admin via GUI(104.28.227[.]105)"

The session associated with the configuration download was established from an external IP address flagged as “malicious” by security vendors with a local account already present on the device. All of these new findings from the attacker’s actions can now be utilized as IOCs to scope available FortiGate logs to determine any other leads.

By correlating activity with the known malicious IP addresses, investigators identified the true entry point: administrative SSO logins to the FortiGate appliance with valid accounts. Another important detail was that there was no evidence of brute-forcing activity for these local accounts. The initial access was established approximately two weeks before any subsequent malicious activity, indicating the attacker used this time to secure consistent access to the environment via the FortiGate device.

Actions such as changing configurations, creating accounts, and downloading configurations might seem harmless individually. However, when viewed together, these activities established a clear pattern consistent with the exploitation of CVE-2025-59718 that facilitated authentication bypass.

Once this groundwork was established through persistence mechanisms and discovery, attackers began authenticating into the environment with their newly created accounts via the SSL VPN connections that led us to investigate the FortiGate device in the first place. These sessions effectively transformed the firewall into an ingress point into the internal network, allowing attackers to move beyond the edge device.

This investigation highlights a common reality in incident response where the first indicator of suspicious activity is rarely the beginning of the story. Instead, responders are often working from a point somewhere in the middle, tasked with reconstructing attacker behavior and peeling back layers of activity to uncover how access was first obtained. 

By following the digital breadcrumbs left behind within available evidence sources, investigators were able to trace the intrusion back to its origin. This process emphasizes the importance of working backward through artifacts and telemetry, recognizing that each piece of data may lead to an earlier stage of attacker activity.

Network edge devices such as firewalls and VPN appliances are often the main vectors of initial access. Despite being critical infrastructure in modern environments, full visibility is rarely achieved in comparison to monitored endpoints. These edge devices can provide valuable evidence during investigations and reveal how initial access went unnoticed.

Conclusion: Key takeaways for defenders

The human element of investigation is crucial. Effective investigations demand a mindset of curiosity; on one side the willingness to dig deeper, and on the other, the ability to look at the big picture. At face value these can seem contradictory, but each facilitates a specific role within an incident response investigation.

Curiosity is what drives responders to grapple with the initial evidence, question assumptions, and identify which threads are worth pulling. It allows responders to move beyond surface-level observations and begin forming hypotheses about what may have occurred. The willingness to dive deeper is what turns those hypotheses into answers. Rather than stopping at the first suspicious event, responders must continue pivoting across logs, correlating activity, and tracing actions further back in time. At the same time, maintaining a big-picture perspective is critical. Individual artifacts or events may appear benign in isolation but when viewed chronologically the attacker behavior emerges.

Looking past any specific incident response methodology, visibility into the environment is essential. Even the strongest investigative approach is limited without access to the right telemetry, thus preventing responders from fully reconstructing an intrusion. In particular, as seen within this investigation, visibility into edge device activity can play a crucial role in unraveling IAV. The network edge is a hostile environment yet is frequently less monitored.

As is often the case with externally facing services and devices, the network edge is constantly targeted. Due to the sheer volume of persistent targeting, this environment can prove difficult to monitor for successful malicious intrusions. Implementing centralized syslog monitoring across these edge devices can close these visibility gaps. It can provide a real-time audit trail of connection attempts, configuration changes, and potential exploit signatures that occur before a threat reaches the internal network.

By effectively pulling on each investigative thread and ensuring visibility across both internal systems and edge devices, defenders can uncover compromises that might otherwise remain hidden. Often, the path to the beginning of the intrusion is already present; it simply requires knowing where, and how, to look.

Detection coverage for Rapid7 customers

Rapid7 actively monitors for emerging threats and leverages evidence from incident response engagements to develop new detection capabilities. Detections have been created and implemented by Rapid7 to pinpoint both exploitation attempts and post-exploitation activities related to FortiGate CVE-2025-59718. For InsightIDR and MDR customers, these detections alert on attacker activity consistent with the techniques described in this blog, enabling earlier identification and response before an intrusion can escalate further.

Detections:

  • Potential Exploitation – FortiGate Admin SSO Login and Config Download via External IP

  • Exfiltration – FortiGate Config Downloaded Using GUI via External IP

  • Suspicious Authentication – FortiGate SSO Login via External IP

Mitigation guidance

Please refer to our initial blog from December, 2025.

MITRE ATT&CK Techniques

Tactic

Technique

Details

Initial Access

Exploit Public-Facing Application (T1190)

Exploitation of vulnerability CVE-2025-59718 on FortiGate firewalls.

Persistence

Create Account (T1136)

Creation of local accounts on FortiGate firewalls.

Persistence and Initial Access

Valid Accounts (T1078)

Use of created accounts and compromised accounts for SSL VPN and RDP authentication.

Defense Evasion

Impair Defenses (T1562)

Firewall rules added to allow for attacker access.

Credential Access

OS Credential Dumping (T1003)

Execution of Mimikatz targeting the local system and Windows Registry hives containing credentials.

Discovery

System Network Configuration Discovery (T1016)

Download of FortiGate firewall configuration files containing sensitive networking information.

Discovery

Network Service Scanning (T1046)

Execution of network scanning tools such as Advanced_Port_Scanner to scan internal IP addresses over SMB protocol.

Lateral Movement

Remote Services (T1021)

Use of Remote Desktop Protocol (RDP).

Execution

Service Execution (T1569.002)

Remote execution of the sysinternals tool PsExec to test credentials against an impacted system.

Indicators of compromise (IOCs)

IOC

Description

Advanced_IP_Scanner_2.5.4594.1.exe

Advanced IP Scanner tool utilized by the attacker.

advanced_ip_scanner.exe 

Advanced IP Scanner tool utilized by the attacker.

mimikatz.exe

An open-source post-exploitation tool utilized by the attacker to extract sensitive authentication credentials.

Advanced_port_scanner_2.5.3869.exe

An open-source network utility utilized by the attacker to quickly map active devices and identify open ports.

23.163.8[.]21

Attacker IP address that targeted FortiGate device.

45.32.216[.]250

IP address used by the attacker during FortiGate configuration changes.

45.84.107[.]17

IP address identified in malicious interaction with SSLVPN.

45.80.186[.]84

IP address identified in malicious interaction with SSLVPN.

185.219.157[.]127

IP address identified in malicious interaction with SSLVPN.

185.175.59[.]238

IP address identified in malicious interaction with SSLVPN.

198.98.54[.]209

Attacker IP address that targeted FortiGate device and SSO login.

45.80.184[.]229

Attacker IP address that targeted FortiGate device and SSLVPN.

45.80.184[.]241

Attacker IP address that targeted FortiGate device and SSLVPN.

42.200.230[.]178

Attacker IP address that targeted FortiGate device and SSLVPN.

103.20.235[.]155

IP address identified in malicious authentications to SSO login.

104.28.227[.]105

IP address identified in attacker download of FortiGate configuration file.

The Attack Cycle is Accelerating: Announcing the Rapid7 2026 Global Threat Landscape Report

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/tr-accelerating-attack-cycle-2026-global-threat-landscape-report

The predictive window has collapsed.

In 2025, high-impact vulnerabilities weren’t quietly accumulating risk. They were operationalized, and often within days.

Today, Rapid7 Labs released the 2026 Global Threat Landscape Report, an in-depth analysis of how attacker behavior is evolving across vulnerability exploitation, ransomware operations, identity abuse, and AI-driven tradecraft. The data shows a clear pattern: exposure is being identified and weaponized faster than most organizations are set up to defend.

From disclosure to exploitation in days, not weeks

In 2025, confirmed exploitation of newly disclosed CVSS 7–10 vulnerabilities increased 105% year over year, rising from 71 to 146. The median time from publication to inclusion in CISA’s Known Exploited Vulnerabilities list fell from 8.5 days to 5.0 days.

At the same time, the number of high-probability vulnerabilities that remained unexploited dropped sharply. The buffer that once allowed teams to triage and schedule remediation is shrinking to the point where some severe flaws were seen to have been exploited almost immediately.

The broader trend is unmistakable: vulnerability management programs built around reactive remediation cycles are struggling to keep pace with adversaries operating at machine speed.

Cybercrime as a structured market

Cybercrime in 2025 no longer resembles chaotic hacking. It resembles platform capitalism.

The report highlights how the underground economy now mirrors legitimate SaaS ecosystems. Initial Access Brokers obtain and validate network footholds. Ransomware operators focus on encryption and extortion. Infostealer operators sell subscription-style access to fresh credential logs.

This specialization lowers barriers to entry and increases scale creating a supply chain in which access is acquired, packaged, priced, and sold to anyone who wants it. 

Ransomware is a good example of this business maturity. It was present in 42% of Rapid7 MDR investigations in 2025 with leak posts increasing 46.4% year over year, and the number of active groups growing from 102 to 140. That kind of growth is anything but random or coincidental: it is an indication of systemic changes to the ransomware ecosystem indicating growing sophistication, specialization, and, ultimately, risk. 

Logging in, not breaking in

Authentication-based attacks remain incredibly common as the lack of consistency across organizations can lead to easy exploitation. Valid accounts without multi-factor authentication (MFA) were responsible for 43.9% of incidents over that year. Rather than forcing their way past defenses, attackers increasingly authenticate with stolen credentials, hijacked sessions, or abused tokens. This is where the increase in AI-driven attacks is particularly acute with the benefits generative AI can play in improving the maturity and sophistication of social engineering attacks. 

As enterprises extend trust across cloud platforms, SaaS ecosystems, APIs, and remote work environments, authentication systems have become the backbone of operational control. This represents a structural shift with the control layer of cyber risk moving away from network perimeters toward authentication flows.

Attacks are using reliable vectors, just at alarming speeds

One hallmark of the attack landscape in 2025 was the use of tried and true attack vectors rather than novel exploits and zero-day vulnerabilities. CVE disclosures continued to climb last year, but confirmed exploitation clustered around dependable weakness types like deserialization, authentication bypass, and memory corruption vulnerabilities.

Attackers are targeting flaws that enable pre-authentication access, repeatable execution, and rapid data theft. They are not, necessarily, chasing every vulnerability. Just the ones they deem reliable. This pattern reinforces a key theme of the report: exploitability and context matter more than raw volume.

AI as an accelerant

AI is serving as a force multiplier and an expanding attack surface at the same time. 

Generative AI is accelerating established attack methods by reducing the time, skill, and coordination previously required to execute them at scale. Rather than introducing entirely new categories of exploitation, threat actors are integrating AI into existing workflows to industrialize phishing, automate reconnaissance, and refine malicious scripts with greater speed and precision. 

AI-assisted phishing campaigns were more polished and tailored to specific industries or executive roles, reflecting a measurable improvement in personalization and believability. They accelerated open-source intelligence collection to create details from fragmented data. AI was used to troubleshoot malware development in near real time, effectively compressing the cycle between initial research and malware deployment. The result is not radical technical innovation, but efficiency, speed, and fewer missed opportunities. 

Meanwhile, AI platforms themselves are emerging as targets with model servers, orchestration frameworks, and token-based integrations, inheriting familiar weaknesses such as unsafe deserialization and weak authentication. As organizations operationalize AI quickly, governance gaps create new high-impact pathways to risk.

The geography of attacks

When it comes to targeted regions, no area of the globe represents a better convergence of exposure and financial opportunity than North America. Organizations on this continent accounted for 82.04% of observed incidents, with the United States representing roughly 70% of leak posts on ransomware leak sites. Manufacturing, business services, and retail were among the most targeted industries as these sectors often combine operational dependence, sensitive data, and financial leverage making them fat targets for attackers looking for reliability not only in their attack vectors, but in gains available from their chosen targets. 

Across criminal and state-aligned activity, attackers are converging on identity systems, edge infrastructure, collaboration platforms, and cloud control planes where trust, scale, and business continuity intersect.

What this means for security leaders

There is a sobering reality in this year’s data: the underlying weaknesses remain familiar. Weak credentials. Social engineering. Exposed services. Unpatched edge infrastructure.

What has changed is the speed.

Security programs can no longer rely on moving slightly faster than attackers. The model must shift toward reducing exposure before it is operationalized.

That means:

  • Continuous exposure visibility with contextual prioritization

  • Strong MFA enforcement and hardened identity controls

  • Protected and monitored edge infrastructure

  • Governance around AI systems and integrations

  • AI-enabled security workflows capable of matching attacker velocity

The organizations that maintain clear, continuous insight into their exposure – and reduce it before it is monetized – will be best positioned to manage risk in this accelerated cycle.

The question is no longer whether exposure exists.
It is whether you can reduce it before attackers capitalize on it.

Read the full Rapid7 2026 Threat Landscape Report to explore the data and strategic implications in detail.

Introducing Hacktics and Telemetry, a Podcast from Rapid7 Labs

Post Syndicated from Douglas McKee original https://www.rapid7.com/blog/post/tr-introducing-hacktics-telemetry-podcast-rapid7-labs

If you spend your days building, shipping, defending, or fixing systems, you already know how this goes. A new technique shows up in a research thread, someone drops a “has anyone checked if we’re exposed?” comment, and suddenly you’re juggling risk, patches, logging gaps, and whatever tool is in the blast radius this week.

That day-to-day reality is why Rapid7 Labs is launching Hacktics and Telemetry, a bi-weekly video and audio podcast with episodes built to fit into a lunch break or a commute. It’s hosted by Rapid7’s Douglas McKee, bringing to the pod years of deep technical and leadership experience, then co-hosted by Jonah ‘CryptoCat’ Burgess – a strong researcher with a solid pulse on the cybersecurity community.

The format stays consistent on purpose. Each episode starts with a scan of what’s emerging, shifts into a guest conversation, then closes with a short segment that ties the story back to mitigation and tooling. The goal is simple: move past theory, show what’s happening with real examples, and leave you with something you can act on.

Episode 1: OpenClaw Risks, RCEs, and Metasploit Pro Updates

Doug and Jonah open by digging into two AI-centric stories from the past week. The first is PhoneLeak, described as data exfiltration in Gemini via phone call. It’s the kind of uncomfortable example that forces practical questions: how do you defend against mobile clickjacking when it’s disguised as a routine CAPTCHA? When an AI assistant has deep extensions into a user’s workspace, how do you prevent malicious prompts from quietly accessing sensitive data like 2FA codes? And perhaps most importantly, how do defenders anticipate and monitor for bizarre, out-of-the-box exfiltration methods—like an AI bypassing SMS confirmations to leak data via DTMF tones on a phone call?

The second story comes from the other side of the AI conversation: an AI agent reportedly identifying an RCE in BeyondTrust remote support, plus discussion of older privileged remote access versions. More automation can mean faster discovery, which shrinks the window between “interesting finding” and “you need to patch this.” That changes how defenders think about exposure, patch prioritization, and what “good enough” means (and looks like) when it comes to monitoring.

In the guest segment, Greg Richardson (Global Advisory CISO & AI Thought Leader, 6 Levers AI) walks through how he uses AI agents in his workflow while keeping control tight. He talks about setting tasks while he sleeps, but the constraints are the point: access is locked down, the agent only touches files he explicitly provides, communication is limited, and token limits help cap the size of any mistake. He also makes a strong case for starting small, with one task at a time, instead of trying to automate dozens of things on day one.

To close out this inaugural episode, the team hits on a SolarWinds Help Desk vulnerability, then shares a quick look at Metasploit Pro 5.0 updates – including more granular payload selection and a walkthrough of the new UI.

If your idea of useful content includes threat trade-offs, concrete mitigations, and a bit of candid “how this actually plays out,” you’re in the right place.

Catch the full episode below:

Critical Cisco Catalyst Vulnerability Exploited in the wild (CVE-2026-20127)

Post Syndicated from Rapid7 Labs original https://www.rapid7.com/blog/post/etr-critical-cisco-catalyst-vulnerability-exploited-in-the-wild-cve-2026-20127

Overview

On February 25, 2026, Cisco disclosed a critical authentication bypass vulnerability in Cisco Catalyst SD‑WAN Controller and Cisco Catalyst SD‑WAN Manager, tracked as CVE‑2026‑20127, that allows an unauthenticated attacker to gain administrative access to affected systems. The Cisco Catalyst SD-WAN Controller and Manager are core components of Cisco’s software-defined wide area networking (SD-WAN) architecture. The issue was originally identified and reported by Australian cybersecurity authorities, who observed real‑world attacks leveraging this flaw. 

Customers running these products must urgently upgrade to a fixed release to prevent further compromise. This vulnerability affects the following deployment types: 

  • On-Prem Deployment

  • Cisco Hosted SD-WAN Cloud

  • Cisco Hosted SD-WAN Cloud – Cisco Managed

  • Cisco Hosted SD-WAN Cloud – FedRAMP Environment

At the time of disclosure, Cisco Talos published a report that outlined how malicious actors in the wild leveraged CVE-2026-20127 to gain initial access, then downgraded the software version on the compromised system for post-exploitation activity. After the targeted system had been downgraded to an older vulnerable firmware release, the attackers exploited CVE-2022-20775 to escalate privileges and gain root access to the system. This exploitation in the wild led CISA to issue an emergency directive to Federal Civilian Executive Branch (FCEB) agencies requiring that patches be installed by 5:00PM ET February 27, 2026.

Mitigation guidance

At the time of the advisory’s publication, Cisco does not recommend any workaround strategies for remediation. Organizations running affected instances of Cisco Catalyst SD-WAN Controller or Cisco Catalyst SD-WAN Manager should prioritize upgrading to a fixed version, as outlined below, to remediate CVE-2026-20127.

  • Affected Cisco Catalyst SD-WAN major version recommendations:

    • 20.11 Release – upgrade to version 20.12.6.1 or above.

    • 20.12.5 Release – upgrade to version 20.12.5.3 or above.

    • 20.12.6 Release – upgrade to version 20.12.6.1 or above.

    • 20.13 Release – upgrade to version 20.15.4.2 or above.

    • 20.14 Release – upgrade to version 20.15.4.2 or above.

    • 20.15 Release – upgrade to version 20.15.4.2 or above.

    • 20.16 Release – upgrade to version 20.18.2.1 or above.

    • 20.18 Release – upgrade to version 20.18.2.1 or above.

    • 20.9 Release – upgrade to version 20.9.8.2 or above (Cisco estimates a patch availability date of February 27, 2026 for this release).

    • Systems running release versions below 20.9 should be migrated to a newer major version with a fix available.

For the latest guidance, refer to the official vendor advisory.

Artifacts/Evidence Sources and IOCs

For any potentially compromised systems, Cisco recommends specific detection and forensic analysis steps to identify exploitation of CVE-2026-20127. According to Cisco, defenders should look for control connection peering events in Cisco Catalyst SD-WAN logs; Cisco states that all peering events will require manual validation to confirm if the events are valid or not, using the following steps:

  • Verify the timestamp of each peering event against known maintenance windows, scheduled configuration changes, and normal operational hours for your environment.

  • Confirm the public IP address corresponds to infrastructure owned or operated by your organization or authorized partners by cross-referencing against asset inventories and authorized IP ranges.

  • Validate the peer system IP matches documented device assignments within your Cisco Catalyst SD-WAN topology.

  • Review the peer type (vmanage, vsmart, vedge, vbond) to ensure it aligns with expected device roles in your deployment.

  • Correlate multiple events from the same source IP or system IP to identify patterns of reconnaissance or persistent access attempts.

  • Cross-reference event timing with authentication logs, change management records, and user activity to establish whether the connection was initiated by authorized personnel.

Rapid7 customers

Exposure Command, InsightVM, and Nexpose

Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-20127 with authenticated checks expected to be available in the Feb 26 content release.

Updates

  • February 25, 2026: Initial publication.

CVE-2026-1731: Critical Unauthenticated Remote Code Execution in BeyondTrust Remote Support (RS) and Privileged Remote Access (PRA)

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/etr-cve-2026-1731-critical-unauthenticated-remote-code-execution-rce-beyondtrust-remote-support-rs-privileged-remote-access-pra

Overview

On February 6, 2026, BeyondTrust released security advisory BT26-02, disclosing a critical pre-authentication Remote Code Execution (RCE) vulnerability affecting its Remote Support (RS) and Privileged Remote Access (PRA) products. Assigned CVE-2026-1731 and a near-maximum CVSSv4 score of 9.9, the flaw allows unauthenticated, remote attackers to execute arbitrary operating system commands in the context of the site user by sending specially crafted requests. The vulnerability affects Remote Support (RS) versions 25.3.1 and prior, as well as Privileged Remote Access (PRA) versions 24.3.4 and prior. 

While BeyondTrust automatically patched SaaS instances on February 2, 2026, self-hosted customers remain at risk until manual updates are applied. The issue was discovered by researchers at Hacktron AI using AI-enabled variant analysis; they identified approximately 8,500 on-premises instances exposed to the internet that could be susceptible to this straightforward exploitation vector. 

While BeyondTrust has not reported active exploitation of CVE-2026-1731 in the wild, the platform’s immense footprint makes it a high-priority target for sophisticated adversaries. BeyondTrust provides identity security services to more than 20,000 customers across over 100 countries, including 75% of the Fortune 100. This ubiquity has attracted state-sponsored actors in the past; notably, the Chinese hacking group “Silk Typhoon” weaponized previous zero-day flaws (CVE-2024-12356 and CVE-2024-12686) to breach the U.S. Treasury Department and access sensitive data related to sanctions, triggering emergency directives from CISA. Rapid7 research later revealed that the exploitation of CVE-2024-12356 actually required chaining it with a critical, then-unknown SQL injection vulnerability in an underlying PostgreSQL tool (CVE-2025-1094). Given this history of targeted attacks against such a widely used platform, these tools remain a critical attack vector that demands immediate defensive action.

Mitigation guidance

A vendor-provided patch is available to remediate CVE-2026-1731 in on-premise deployments.

BeyondTrust Remote Support (RS):

  • Versions 25.3.1 and prior are affected by CVE-2026-1731.

  • CVE-2026-1731 is fixed in 25.3.2 and later.

BeyondTrust Privileged Remote Access (PRA):

  • Versions 24.3.4 and prior are affected by CVE-2026-1731.

  • CVE-2026-1731 is fixed in 25.1.1 and later.

Please read the vendor advisory for the latest guidance.

Rapid7 customers

Exposure Command, InsightVM, and Nexpose

Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-1731 on Remote Support and Privileged Remote Access using authenticated checks expected to be available in today’s (Feb 9) content release.

Chrysalis, Notepad++, and Supply Chain Risk: What it Means, and What to Do Next

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/tr-chrysalis-notepad-supply-chain-risk-next-steps

When Rapid7 published its analysis of the Chrysalis backdoor linked to a compromise of Notepad++ update infrastructure, it raised understandable questions from customers and security teams. The investigation showed that attackers did not exploit a flaw in the application itself. Instead, they compromised the hosting infrastructure used to deliver updates, allowing a highly targeted group to selectively distribute a previously undocumented backdoor associated with the Lotus Blossom APT.

Subsequent reporting from outlets including BleepingComputer, The Register, SecurityWeek, and The Hacker News has helped clarify the scope of the incident. What’s clear is that this was a supply chain attack against distribution infrastructure, not source code. The attackers maintained access for months, redirected update traffic selectively, and limited delivery of the Chrysalis payload to specific targets, helping them stay hidden and focused on espionage rather than mass compromise.

What does the Notepad++ incident mean?

This incident highlights how modern supply chain attacks have evolved. Rather than targeting application code, attackers abused shared hosting infrastructure and weaknesses in update verification to quietly deliver malware. The broader takeaway is that supply chain risk now extends well beyond build systems and repositories. Update mechanisms, hosting providers, and distribution paths have become attractive targets, especially when they sit outside an organization’s direct control.

Was Notepad++ itself compromised?

Based on public statements from the Notepad++ maintainer and independent reporting, there is no evidence that the application’s source code or core development process was compromised. The risk stemmed from the update delivery infrastructure, reinforcing that even trusted software can become a delivery mechanism when upstream systems are abused.

Who was behind the Chrysalis backdoor & Notepad++ attack?

Rapid7 was the first to publish attribution linking this activity to Lotus Blossom, a Chinese state-aligned advanced persistent threat (APT) group. Based on our analysis, we assess with moderate confidence that this group is responsible for the Notepad++ infrastructure compromise and the deployment of the Chrysalis backdoor.

Lotus Blossom has been active since at least 2009 and is known for long-running espionage campaigns targeting government, telecommunications, aviation, critical infrastructure, and media organiations, primarily across Southeast Asia, and more recently, Latin America.

The tactics, tooling, and infrastructure used in this campaign – including the abuse of update infrastructure, the use of selective targeting, and the deployment of custom malware, are consistent with the group’s historical tradecraft. As with any attribution, this conclusion is based on observed behaviors and intelligence correlations, not a single, definitive indicator.

What should organizations do right now?

Based on what we know today, there are several immediate actions organizations should take:

  • Check and update Notepad++ installations. Ensure any instances are running the latest version, which includes improved certificate and signature verification.

  • Review historical telemetry. Even though attacker infrastructure has been taken down, organizations should scan logs and environments going back to October 2025 for indicators of compromise associated with this campaign.

  • Hunt, don’t just scan. This activity was selective and low‑volume. Absence of alerts does not guarantee absence of compromise.

  • Use available intelligence. Rapid7 Intelligence Hub customers have access to the Chrysalis campaign intelligence, along with follow‑up indicators provided by partners such as Kaspersky, to support targeted hunting across endpoints and network telemetry.

Why does this matter beyond Notepad++?

This incident is a case study in how trust is exploited in modern environments. The attackers didn’t rely on zero days or noisy malware. They abused update workflows, hosting relationships, and assumptions about trusted software. That same approach applies across countless tools and platforms used daily inside enterprise environments.

It also reinforces a broader trend we’ve seen over the last year: attackers are patient, selective, and focused on long‑term access rather than immediate impact. That has implications for detection strategies, incident response planning, and supply chain risk management.

What does this mean for software supply chain security?

For defenders, this incident reinforces several lessons:

  • Supply chain security must include distribution and hosting infrastructure, not just source code.

  • Update mechanisms should enforce strong signature and metadata validation by default.

  • Shared hosting environments represent an often overlooked risk, especially for widely deployed tools.

  • Trust in software must be continuously validated, not assumed.

The Chrysalis incident is not just about a single tool or a single campaign. It reflects a broader shift in how advanced threat actors think about access, persistence, and trust. Software supply chains are no longer just a development concern. They are an operational and security concern that extends into hosting providers, update mechanisms, and the assumptions organizations make about what is “safe.”

As attackers continue to favor selective targeting and long‑term access over noisy, large‑scale compromise, defenders need to adapt accordingly. That means moving beyond basic scanning, validating trust continuously, and treating update and distribution infrastructure as part of the attack surface.

Learn more: Watch the full Chrysalis debrief webinar

If you’d like to hear directly from the researchers behind this discovery, watch the full Chrysalis: Inside the Supply Chain Compromise of Notepad++ webinar, now available on BrightTALK. In this detailed session, Christian Beek (Senior Director, Threat Analytics) and Steve Edwards (Director, Threat Intel & Detection Engineering) walk through the full attack chain, from initial compromise to malware behavior, attribution to Lotus Blossom, and what organizations can do right now to assess exposure and strengthen supply chain security. [Watch Now]

Critical Ivanti Endpoint Manager Mobile (EPMM) zero-day exploited in the wild (CVE-2026-1281 & CVE-2026-1340)

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/etr-critical-ivanti-endpoint-manager-mobile-epmm-zero-day-exploited-in-the-wild-eitw-cve-2026-1281-1340

Overview

On January 29, 2026, Ivanti disclosed two new critical vulnerabilities affecting Endpoint Manager Mobile (EPMM): CVE-2026-1281 and CVE-2026-1340. The vendor has indicated that exploitation in the wild has already occurred prior to disclosure. This has been echoed by CISA who added CVE-2026-1281 to their Known Exploited Vulnerabilities (KEV) catalog shortly after the vendor disclosure. As an indication of how critical this development is, CISA has given a “due date” of only 3 days (Due Feb 1, 2026) for organizations, such as federal agencies, to remediate the vulnerabilities before the affected devices must be removed from a network.

While CVE-2026-1281 has been confirmed as exploited in the wild as a zero day, it is unclear if CVE-2026-1340 has also, or if this vulnerability was found separately to CVE-2026-1281. The two critical vulnerabilities are summarized below.

CVE

CVSSv3

CWE

CVE-2026-1281

9.8 (Critical)

Improper Control of Generation of Code (CWE-94)

CVE-2026-1340

9.8 (Critical)

Improper Control of Generation of Code (CWE-94)

Both CVE-2026-1281 and CVE-2026-1340 are described identically by the vendor; they are code injection issues, allowing a remote unauthenticated attacker to execute arbitrary code on an affected device. Based on the vendor’s guidance, the attackers can provide Bash commands as part of a malicious HTTP GET request to the endpoints that service either the “In-House Application Distribution” feature (i.e. /mifs/c/appstore/fob/) or the “Android File Transfer Configuration” feature (i.e. /mifs/c/aftstore/fob/), resulting in arbitrary OS command execution on the target. 

As EPMM is an endpoint management solution for mobile devices, the impact of an attacker compromising the EPMM server is significant. An attacker may be able to access Personally Identifiable Information (PII) regarding mobile device users, such as their names and email addresses, but also their mobile device information, such as their phone numbers, GPS information, and other sensitive unique identification information. This is in addition to the privileged position an attacker will have on the EPMM device itself, which may allow for lateral movement within the compromised network.
Given the nature of the product, EPMM is a high-profile target. It has been repeatedly targeted by zero-day vulnerabilities in the past. In 2023 the product was exploited in the wild via CVE-2023-35078, and again in 2025 via an exploit chain of CVE-2025-4427 and CVE-2025-4428. As of January 30, 2026, a public working proof-of-concept exploit for remote code execution is available. Organizations running EPMM are urged to act quickly and follow the vendor guidance to remediate these issues.

Threat hunting 

The following vendor supplied regular expression can be used to search the HTTP daemon’s log files for evidence of potential exploitation of CVE-2026-1281 and CVE-2026-1340:

^(?!127\.0\.0\.1:\d+ .*$).*?\/mifs\/c\/(aft|app)store\/fob\/.*?404

Mitigation guidance

A vendor supplied update is available to remediate both vulnerabilities.

The following affected versions of Ivanti EPMM are remediated via the RPM 12.x.0.x patch:

  • Versions 12.7.0.0 and below

  • Versions 12.6.0.0 and below

  • Versions 12.5.0.0 and below

The following affected versions of Ivanti EPMM are remediated via the RPM 12.x.1.x patch:

  • Versions 12.6.1.0 and below

  • Versions 12.5.1.0 and below

Customers are advised to update to the latest remediated version of EPMM, on an emergency basis outside of normal patching cycles, as exploitation in-the-wild is already occurring.

For the latest mitigation guidance for Ivanti EPMM, please refer to the vendor’s security advisory. In addition to remediation, the vendor has provided additional threat hunting guidance.

Rapid7 customers

Exposure Command, InsightVM, and Nexpose

Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-1281 and CVE-2026-1340 with authenticated vulnerability checks expected to be available in today’s (Jan 30) content release. Note that the “Potential” category must be enabled in the scan template to run the checks.

Updates

  • January 30, 2026: Added reference to the watchTowr technical analysis and proof-of-concept exploit.

Multiple Critical SolarWinds Web Help Desk Vulnerabilities: CVE-2025-40551, CVE-2025-40552, CVE-2025-40553, CVE-2025-40554

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/etr-multiple-critical-solarwinds-web-help-desk-vulnerabilities-cve-2025-40551-40552-40553-40554

Overview

On January 28, 2026, SolarWinds published an advisory for multiple new vulnerabilities affecting their Web Help Desk product. Web Help Desk is an IT help desk ticketing and asset management software solution. Of the six new CVEs disclosed in the advisory, four are critical, and allow a remote attacker to either achieve unauthenticated remote code execution (RCE) or bypass authentication. 

As of this writing, there is currently no known in-the-wild exploitation occurring. However, we expect this to change as and when technical details become available. Notably, this product has been featured on CISA’s Known Exploited Vulnerabilities (KEV) list twice in the past, circa 2024, indicating that it is a target for real-world attackers.

The six vulnerabilities are summarized below.

CVE

CVSSv3

CWE

CVE-2025-40551

9.8 (Critical)

Deserialization of Untrusted Data (CWE-502)

CVE-2025-40552

9.8 (Critical)

Weak Authentication (CWE-1390)

CVE-2025-40553

9.8 (Critical)

Deserialization of Untrusted Data (CWE-502)

CVE-2025-40554

9.8 (Critical)

Weak Authentication (CWE-1390)

CVE-2025-40536

8.1 (High)

Protection Mechanism Failure (CWE-693)

CVE-2025-40537

7.5 (High)

Use of Hard-coded Credentials (CWE-798)

Technical overview

Both CVE-2025-40551 and CVE-2025-40553 are critical deserialization of untrusted data vulnerabilities that allow a remote unauthenticated attacker to achieve RCE on a target system and execute payloads such as arbitrary OS command execution. RCE via deserialization is a highly reliable vector for attackers to leverage, and as these vulnerabilities are exploitable without authentication, the impact of either of these two vulnerabilities is significant.

The other two critical vulnerabilities, CVE-2025-40552 and CVE-2025-40554, are authentication bypasses that allow a remote unauthenticated attacker to execute actions or methods on a target system which are intended to be gated by authentication. Based upon the vendor supplied CVSS scores for these two authentication bypass vulnerabilities, the impact is equivalent to the two RCE deserialization vulnerabilities, likely meaning they can also be leveraged for RCE.

In addition to the four critical vulnerabilities, two high severity vulnerabilities were also disclosed. CVE-2025-40536 is an access control bypass vulnerability, allowing an attacker to access functionality on the target system that is intended to be restricted to authenticated users. Separately, CVE-2025-40537 may, under certain conditions, allow access to some administrative functionality on the target system due to the existence of hardcoded credentials. 

Mitigation guidance

A vendor supplied update is available to remediate all six vulnerabilities: CVE-2025-40551, CVE-2025-40552, CVE-2025-40553, CVE-2025-40554, CVE-2025-40536, and CVE-2025-40537. The following product versions are affected:

  • SolarWinds Web Help Desk versions 12.8.8 Hotfix 1 and below.

Customers are advised to update to the latest Web Help Desk version, 2026.1, on an urgent basis outside of normal patching cycles.

For the latest mitigation guidance for SolarWinds Web Help Desk, please refer to the vendor’s security advisory.

Rapid7 customers

Exposure Command, InsightVM, and Nexpose customers can assess their exposure to CVE-2025-40551, CVE-2025-40552, CVE-2025-40553 and CVE-2025-40554 with remote vulnerability checks expected to be available in today’s (28 Jan) content release.

Ni8mare and N8scape flaws among multiple critical vulnerabilities affecting n8n

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/etr-ni8mare-n8scape-flaws-multiple-critical-vulnerabilities-affecting-n8n

Overview

On November 18, 2025, a patched release was published for a critical unauthenticated file read vulnerability in n8n, a popular piece of automation software. The advisory for this vulnerability, CVE-2026-21858, was subsequently published on January 7, 2026; the vulnerability holds a CVSS score of 10.0. If a server has a custom configured web form that implements file uploads with no validation of content type, an attacker can overwrite an internal JSON object to read arbitrary files and, in some cases, establish remote code execution. This vulnerability has been dubbed “Ni8mare” by the finders. 

The finders, Cyera, published a technical blog post about the vulnerability on January 7, 2026, and a separate technical analysis and proof-of-concept (PoC) exploit were published by third-party security researcher Valentin Lobstein the same day. The Cyera writeup demonstrates CVE-2026-21858, while the third-party exploit also leverages CVE-2025-68613, an authenticated expression language injection vulnerability in n8n, for remote code execution. Additional authenticated vulnerabilities, tracked as CVE-2025-68613, CVE-2025-68668, CVE-2025-68697, and CVE-2026-21877 can be chained with the unauthenticated vulnerability CVE-2026-21858 for code execution or arbitrary file write on specific affected versions of n8n.

In total there are five CVEs that n8n users should be aware of:

CVE Number

Published Date

CVSS

Description

Leveraged in PoC?

CVE-2026-21858 (Ni8mare)

01/07/2026

10.0 (NVD score)

Certain form-based workflows are vulnerable to improper file handling that can result in arbitrary file read. When exploited, attackers can establish administrator-level access to n8n.

Yes

CVE-2026-21877

01/07/2026

9.9 (NVD score)

Under certain conditions, authenticated n8n users may be able to cause untrusted code to be executed by the n8n service.

No

CVE-2025-68613

12/19/2025

8.8 (NVD score)

A vulnerability in n8n’s expression evaluation system allows authenticated users to execute arbitrary system commands through crafted expressions in workflow parameters.

Yes

CVE-2025-68668 (N8scape)

12/26/2025

9.9 (NVD score)

A sandbox bypass vulnerability exists in the n8n Python Code node that uses Pyodide. An authenticated user with permission to create or modify workflows can exploit this vulnerability to execute arbitrary commands on the host system running n8n in the context of the service user.

No

CVE-2025-68697

12/26/2025

5.4 (NVD score)

In self-hosted n8n instances where the Code node runs in legacy (non-task-runner) JavaScript execution mode, authenticated users with workflow editing access can invoke internal helper functions from within the Code node. This permits reading and writing files on the host.

No

Technical overview

CVE-2026-21858: “Unauthenticated File Access via Improper Webhook Request Handling”

This is the primary access vector for the n8n exploit chain and holds a maximum CVSS score of 10.0. It is a critical unauthenticated file read vulnerability that occurs when custom web forms implement file uploads without validating the content type. By exploiting this flaw, an attacker can overwrite an internal JSON object to read arbitrary files from the server. This capability may be leveraged to forge an administrator session token and exploit subsequent authenticated vulnerabilities for code execution.

CVE-2025-68613: “Remote Code Execution via Expression Injection”

This vulnerability is characterized as an authenticated expression language injection flaw. While it requires an established session to exploit, it can be chained with CVE-2026-21858 to achieve remote code execution. It affects n8n versions starting at 0.211.0 and below 1.20.4. Attackers can leverage this flaw by injecting malicious expression language commands once they have gained a foothold as an administrator.

CVE-2025-68668: “Arbitrary Command Execution in Pyodide based Python Code node”

Affecting n8n versions between 1.0.0 and 2.0.0, this is an authenticated vulnerability used for secondary exploitation. Depending on the specific configuration of the affected version, it allows an attacker to execute arbitrary OS commands. Because it requires authentication, it is used on a case-by-case basis after an initial breach has compromised the management interface.

CVE-2025-68697: “Legacy Code node enables file read/write in self-hosted n8n”

CVE-2025-68697 is an authenticated vulnerability that facilitates arbitrary file read/write in the context of the n8n process when exploited. Per the advisory, systems are vulnerable when the Code node runs in legacy (non-task-runner) JavaScript execution mode. CVE-2025-68697 specifically impacts n8n versions ranging from 1.2.1 up to 2.0.0, though n8n version 1.2.1 and higher automatically prevents read/write access to the `.n8n` directory by default. As a result, exploitation of CVE-2025-68697 is likely to require a more bespoke strategy for each specific target, making it a less likely vulnerability to be exploited as a secondary chained bug with CVE-2026-21858.

CVE-2026-21877: “RCE via Arbitrary File Write”

This vulnerability has a CVSS score of 9.9 and affects both self-hosted and cloud versions of n8n. It allows for remote code execution within n8n versions 0.123.0 through 1.121.3. Although it is an authenticated vulnerability, its high severity stems from its ability to grant an attacker full system control once they have bypassed initial authentication using the CVE-2026-21858 file read flaw.

Mitigation guidance

Organizations running self-hosted instances of n8n should prioritize upgrading to a version at or above 1.121.0 immediately to remediate the unauthenticated initial access vulnerability CVE-2026-21858.

According to the vendor, the following versions are affected:

  • CVE-2026-21858: Versions at or above 1.65.0 and below 1.121.0.

  • CVE-2025-68613: Versions at or above 0.211.0 and below 1.20.4.

  • CVE-2025-68668: Versions at or above 1.0.0 and below 2.0.0.

  • CVE-2025-68697: Versions at or above 1.2.1 and below 2.0.0.

  • CVE-2026-21877: Versions at or above 0.123.0 and below 1.121.3.

For the latest mitigation guidance, please refer to the vendor’s security advisories.

Rapid7 customers

Exposure Command, InsightVM, and Nexpose

Exposure Command and InsightVM customers can assess exposure to CVE-2026-21858, CVE-2025-68613, CVE-2025-68668, CVE-2025-68697, and CVE-2026-21877 with vulnerability checks expected to be available in the January 9, 2026 content release.

Updates

  • January 8, 2026: Initial publication.

MongoBleed CVE-2025-14847: Critical Memory Leak in MongoDB Allowing Attackers to Extract Sensitive Data

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/etr-mongobleed-cve-2025-1484-critical-memory-leak-in-mongodb-allowing-attackers-to-extract-sensitive-data

Overview

On December 19, 2025, MongoDB Inc. disclosed a critical new vulnerability, CVE-2025-14847, which has since been dubbed MongoBleed. This vulnerability is a high-severity unauthenticated memory leak affecting MongoDB, one of the world’s most popular document-oriented databases. While initially identified as a data exposure flaw, the severity is underscored by the fact that it allows attackers to bypass authentication entirely to extract sensitive information directly from server memory. On December 26, 2025, public proof-of-concept (PoC) exploit code was published and on December 29th, 2025 exploitation in-the-wild has been confirmed.

While CVE-2025-14847 is rated as a high-severity vulnerability, CVSS 8.7, its impact is critical. Successful exploitation allows a remote, unauthenticated attacker to “bleed” uninitialized heap memory from the database server by manipulating Zlib-compressed network packets. This memory often contains high-value secrets such as cleartext credentials, authentication tokens, and sensitive customer data from other concurrent sessions. Because the vulnerability returns “uninitialized heap memory,” an attacker cannot target specific credentials or data records with precision; they must instead rely on repeated exploitation attempts and chance to capture sensitive information.

The vulnerability specifically affects MongoDB servers configured to use the Zlib compression algorithm for network messages, which is a common configuration in many production environments. It affects a wide range of versions, including the 4.4, 5.0, 6.0, 7.0, and 8.0 branches. Older, End-of-Life (EOL) versions are also believed to be vulnerable but will not receive official patches, leaving users of legacy systems at significant continued risk.

As of this writing, the public PoC has been successfully verified by Rapid7 Labs. Unlike scenarios where valid exploits are initially scarce, the exploit for MongoBleed is functional and reliable.

Organizations running self-managed MongoDB instances are urged to remediate this vulnerability on an urgent basis, outside of normal patch cycles. Given the nature of the leak, simply patching is insufficient; organizations are advised to also rotate all database and application credentials that may have been exposed prior to remediation.

Mitigation guidance

CVE-2025-14847 affects a wide range of versions, including the 4.4, 5.0, 6.0, 7.0, and 8.0 branches. Older, End-of-Life (EOL) versions are also believed to be vulnerable but will not receive official patches, leaving users of legacy systems at significant continued risk. Organizations managing their own MongoDB instances should prioritize upgrading to the fixed versions released by the vendor (e.g., 8.0.4, 7.0.16, 6.0.20, etc.) immediately. This is the only complete remediation for the vulnerability. 

If an immediate upgrade is not feasible, or if the organization is running an End-of-Life (EOL) version that will not receive a patch, the risk can be effectively mitigated by disabling the Zlib network compressor in the server configuration. This prevents the specific memory allocation path used by the exploit.

In addition, because CVE-2025-14847 allows for the exfiltration of credentials and session tokens from server memory, patching alone is insufficient to ensure security. Administrators should assume that any secrets residing in the database memory prior to patching may have been compromised; therefore, all database passwords, API keys, and application secrets should be rotated immediately after the vulnerability is remediated. 

Rapid7 customers

Exposure Command, InsightVM, and Nexpose

Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2025-14847 with a vulnerability check expected to be available in today’s (Dec 29) content release.

Intelligence Hub

Customers leveraging Rapid7’s Intelligence Hub can track the latest developments surrounding CVE-2025-14847, including a Suricata rule. 

Rapid7 observations

Rapid7 Labs has become aware of a new exploitation tool that streamlines the extraction of sensitive data from vulnerable MongoDB instances. This utility introduces a graphical user interface that allows an attacker to either batch-dump 10MB of memory or monitor the extraction process via a live visual feed. Rapid7 Labs has confirmed the tool operates as described, as demonstrated in the video below.

Click to view in new tab

Detection and Hunting

Velociraptor 

Velociraptor published a Linux.Detection.CVE202514847.MongoBleed hunting artifact written by Eric Capuano designed to detect indicators related to CVE-2025-14847 memory leakage activity. This artifact enables defenders to proactively identify suspicious network or process behaviors consistent with mangled Zlib protocol abuse.

Updates

  • December 29, 2025: Initial publication

  • December 29, 2025: “Rapid7 Observations” section added with video

  • December 29, 2025: Added exploitation confirmation

Update on Spring4Shell’s Impact on Rapid7 Solutions and Systems

Post Syndicated from Rapid7 original https://blog.rapid7.com/2022/04/01/update-on-spring4shells-impact-on-rapid7-solutions-and-systems/

Update on Spring4Shell’s Impact on Rapid7 Solutions and Systems

We have been continuously monitoring for Spring4Shell exploit attempts in our environment and have been urgently investigating the implications for our corporate and production systems. We are actively remediating vulnerabilities as we find them and monitoring for any anomalous activity in our environment.

We will update this page as we learn more. At this time, customers do not need to take any action.

Further reading and recommendations

Our Emergent Threat Response team has put together a detailed blog post with general guidance about how to mitigate and remediate Spring4Shell. We will continue updating that post as we learn more about Spring4Shell and new remediation and mitigation approaches.

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.

Russia/Ukraine Conflict: What Is Rapid7 Doing to Protect My Organization?

Post Syndicated from Rapid7 original https://blog.rapid7.com/2022/02/25/russia-ukraine-conflict-what-is-rapid7-doing-to-protect-my-organization/

Russia/Ukraine Conflict: What Is Rapid7 Doing to Protect My Organization?

Rapid7 is monitoring the escalating conflict in Ukraine, and we have provided a blog on the various attack vectors organizations may see, as well as guidance on mitigations and remediations.

To assist with your preparation and response efforts, Rapid7 is continuously integrating into our products the most up-to-date threat intelligence — both consumed and curated — which are monitoring for new attack vectors and intelligence in order to alert on attacker behaviors that are associated with various Advanced Persistent Threat (APT) groups within InsightIDR.

If you are a Managed Detection & Response (MDR) customer, our global SOC teams are monitoring your environment 24/7 with a high degree of diligence, and as standard procedure, any verified suspicious activity will be investigated and reported to you with expediency. Considering the current crisis, we have placed a special emphasis on the most relevant APT groups, and we are closely monitoring a wide breadth of sources to make use of any newly created and verified indicators.

Keeping software patched against known vulnerabilities is an important first line of defense against attackers. On January 11, 2022, the Cybersecurity & Infrastructure Security Agency (CISA) published Alert AA22-011A: Understanding and Mitigating Russian State-Sponsored Cyber Threats to US Critical Infrastructure, listing several vulnerabilities known to be exploited by Russian threat actors.

InsightVM and Nexpose have checks for the CVEs called out in this alert. These vulnerabilities are included in InsightVM’s Threat Feed Dashboard (see the Assets With Actively Targeted Vulnerabilities card and the Most Common Actively Targeted Vulnerabilities card), along with other vulnerabilities known to be exploited in the wild.

Useful resources

Staying Secure in a Global Cyber Conflict

Post Syndicated from Rapid7 original https://blog.rapid7.com/2022/02/25/russia-ukraine-staying-secure-in-a-global-cyber-conflict/

Staying Secure in a Global Cyber Conflict

Now that Russia has begun its armed invasion of Ukraine, we should expect increasing risks of cybersecurity attacks and incidents, either as spillover from cyberattacks targeting Ukraine or direct attacks against actors supporting Ukraine.

Any state-sponsored Russian attacks aiming to support the Russian invasion of Ukraine, or to retaliate for US, NATO, or other foreign measures taken in response to the Russian invasion of Ukraine, are most likely to be destructive or disruptive in nature rather than aiming to steal data. This blog discusses the types of attacks organizations may see — including distributed denial of service (DDoS), website defacements, and the use of ransomware or destructive malware — and recommends steps for their mitigation or remediation.

As we have stated before, we do not believe organizations need to panic. But as per guidance from numerous governments, we do believe it is wise to be extra vigilant at this time. Rapid7 will continue to monitor the cybersecurity risks, both internally and for our Managed Detection and Response (MDR) customers as the situation evolves. We will post updates as relevant and suggest subscription to our blog to see them as they are posted.

Malware

One of the most concerning possibilities is the risk of a destructive malware attack on the US, NATO members, or other foreign countries. This could take the form of a direct attack or spillover from an attack on Ukraine, such as the 2017 NotPetya operation that targeted Ukraine and spread to other parts of the globe. Cybersecurity researchers have just discovered a new data wiping malware, dubbed HermeticWiper (AKA KillDisk.NCV), that infected hundreds of Ukrainian machines in the last two months. This seems to be a custom-written malware that corrupts the Master Boot Record (MBR), resulting in boot failure. This malware, like NotPetya, is intended to be destructive and will cripple the assets that it infects.

As always, the best malware prevention is to avoid infection in the first place — a risk we can minimize by ensuring that assets are up to date and use strong access controls, including multi-factor authentication. Additionally, it is crucial to have an incident response plan in place for the worst-case scenario, as well as a business continuity plan — including failover infrastructure if possible — for business-critical assets.

DDoS

There have already been reports of DDoS attacks on Ukrainian websites, and Russia has historically used DDoS in support of operations against other former Soviet republics, such as Georgia, in the past. Given this context, it is plausible that state-sponsored Russian actors would use DDoS if they choose to retaliate in response to measures taken against Russia for the invasion of Ukraine, such as sanctions or cyber operations from NATO countries.

While DDoS does not receive the same level of attention as some other forms of attack, it can still have significant impacts to business operations. DDoS mitigations can include reduction of attack surface area via Content Distribution Networks or load balancers, as well as the use of Access Control Lists and firewalls to drop traffic coming from attacker nodes.

Phishing campaigns

Russian state-sponsored actors are also well known for engaging in spear-phishing attacks, specifically with compromised valid accounts. Defenders should ensure strong spam filtering and attachment scanning is in place. Educating end users of the dangers of phishing and regularly running phishing campaigns will also help mitigate this issue.

State-sponsored, APT-style groups are not the only relevant threats. In times of crisis, it is common to see phishing attacks linking to malicious websites masquerading as news, aid groups, or other seemingly relevant content. Opportunistic scammers and other bad actors will attempt to take advantage of our human nature when curiosity, anxiety, and desire to help can make people less suspicious. Remain vigilant and avoid clicking unknown links or opening attachments — basic cyber hygiene that can be forgotten when emotions run high.

Brute-force attacks

According to a report from the NSA, CISA, FBI, and NCSC, “From mid-2019 through early 2021, Russian General Staff Main Intelligence Directorate (GRU) … conduct[ed] widespread, distributed, and anonymized brute-force access attempts against hundreds of government and private sector targets worldwide.” GRU used the discovered credentials to gain access into networks and further used known vulnerabilities such as CVE-2020-0688 and CVE-2020-17144 to increase access.

The best mitigation for these types of attacks is to enable MFA on all systems. Minimize externally facing systems and ensure externally facing systems are fully patched.

Defacement

Ukraine has also been experiencing website defacements, which provide attackers with an opportunity to spread messaging. Website defacement is typically associated with hacktivist activity, but state-sponsored Russian actors could pose as hacktivists in order to disguise Russian state involvement, and spread their strategic communication themes to international audiences by defacing Western websites.

Website defacement often occurs as a result of weak passwords for admin accounts, cross-site scripting, injection, file upload, or vulnerable plugins. This can be managed by limiting the level of access accounts have and enforcing strong passwords. Additionally, looking for places where scripts or iframes could be injected or where SQL injection could occur can help identify vulnerabilities to remediate.

Ransomware

Ransomware could also be used to disrupt foreign targets. Criminals based in Russia were believed to be behind the 2021 ransomware attack on Colonial Pipeline in the United States. Ransomware can have disruptive effects on targets, and the attackers could simply refrain from decrypting files, even if they receive ransom payments, in order to maximize and extend the disruptive impact on victims. Additionally, opportunistic attackers who are actually looking for ransoms will still be on the prowl, and are likely to take advantage of the chaos.

To this end, defenders should:

  • Evaluate asset and application configurations to ensure resilience
  • Double-check visibility into the functioning of business-critical assets
  • Assess incident response processes in the case of an incident

What else should you be doing?

The following activities are mission-critical in times of uncertainty, but they are also best practices in general.

  • Continuous monitoring: Reinforce cybersecurity measures and staff during nights, weekends, and holidays. Threat actors are known to target their victims when there are gaps in “eyes on glass.”
  • Incident response plan: Prepare a dedicated team with a detailed workflow and a contact person that will be available offline in case of a cybersecurity incident.
  • Back up data: Implement data backup procedures of the company networks and systems. Backup procedures should be conducted on a frequent, regular basis for immediate recovery. Also, be sure to store backups offline and check them regularly to ensure they have not been poisoned with malware.
  • Reduce opportunities for attackers: Identify exposures, vulnerabilities, and misconfigurations that can provide opportunities for attackers to gain a foothold in your environment, and apply relevant mitigations or patches. In particular, Russian operators are well known to exploit edge systems. The Cybersecurity and Infrastructure Security Agency (CISA) recently put out an alert listing 13 known vulnerabilities that Russian state-sponsored threat actors use to initially compromise networks. We recommend this as a starting point for focused patching and mitigation.
  • Stay informed: Follow the latest updates and recommendations provided by Rapid7, as well as governmental security entities in specific press releases/alerts from the Ukraine CERT, The Security Service of Ukraine (SSU), and the US CISA.

We expect the situation to be fluid over the coming days and weeks, and security guidance and threats may also evolve as the conflict develops. The measures suggested in this blog will continue to be relevant, and we plan to provide additional information as needed.

In the meantime, you can also check this blog to see how Rapid7 can help you prepare for and respond to cyber attacks. We also recommend organizations check their government’s cybersecurity website for guidance.

Trojan Source CVE-2021-42572: No Panic Necessary

Post Syndicated from boB Rudis original https://blog.rapid7.com/2021/11/04/trojan-source-cve-2021-42572/

What is this thing?

Trojan Source CVE-2021-42572: No Panic Necessary

Researchers at the University of Cambridge and the University of Edinburgh recently published a paper on an attack technique they call “Trojan Source.” The attack targets a weakness in text-encoding standard Unicode—which allows computers to handle text across many different languages—to trick compilers into emitting binaries that do not actually match the logic visible in source code. In other words, what a developer or security analyst sees in source code with their own eyes could be different from how a compiler interprets it—leading, in effect, to an attack that is not easily discernible. This weakness arises from Unicode’s bidirectional “BiDi” algorithm and affects most compilers, or perhaps more accurately, most editing and code review tooling; the idea that source code will be compiled the way it is displayed to the human eye is a fundamental assumption.

How the attack works.

It is possible, and often necessary, to have both left-to-right and right-to-left glyphs appear in the same sentence. A classic example from O’Reilly’s “Unicode Explained” book shows Arabic embedded in an English sentence and the direction readers familiar with both languages will read the section in:

Trojan Source CVE-2021-42572: No Panic Necessary

The official Unicode site also has additional information and examples.

There are a few options available to creators when the need for a document or section of a document to support bidirectional content, one of which is to insert “invisible” control characters that dictate the directionality of text following the directive. This is how the “Trojan Source” attack works. Let’s use one of the examples from the paper to illustrate what’s going on.

Trojan Source CVE-2021-42572: No Panic Necessary

The screenshot above is from the GitHub repository associated with the paper and shows the C language source code that looks like it should not print anything when compiled and run. (Also note that there is a very explicit safety banner, which you should absolutely take very seriously in any source code you see it displayed in).

When we copy that code from the browser and paste it into the popular Sublime Text editor with the Gremlins package installed and enabled, we can see the attempted shenanigans pretty clearly:

Trojan Source CVE-2021-42572: No Panic Necessary

The line number sidebar shows where sneaky directives have been inserted, and the usually invisible content is explicitly highlighted and not interpreted, so you can see what’s actually getting compiled. In this case, one is always “admin” when they run this program. The bottom line is that you cannot fully trust just your eyes without some assistance.

Note that cat Linux command (available on Windows via the Windows Subsystem for Linux and via macOS by installing the GNU version of the utility) can also be used to display these invisible gremlins:

cat -A -v commentint-out.c                                                  #include <stdio.h>$
#include <stdbool.h>$
$
int main() {$
    bool isAdmin = false;$
    /*M-bM-^@M-. } M-bM-^AM-&if (isAdmin)M-bM-^AM-) M-bM-^AM-& begin admins only */$
        printf("You are an admin.\n");$
    /* end admins only M-bM-^@M-. { M-bM-^AM-&*/$
    return 0;$
}$
$

Unfortunately, GitHub’s safety banner and code-editor plugins do not scale very well. Thankfully, Red Hat has come to the rescue with a simple Python script which can help us identify potential issues across an entire codebase with relative ease. It should also be possible to use this script in pre-commit hooks or in CI/CD workflows to prevent malicious code from entering into production.

CVSSv3 9.8?! Orly?!

While this isn’t really a “vulnerability” in the traditional sense of the word, it’s been assigned CVE-2021-42574 and given a “Critical” CVSSv3 score of 9.8. (The “PetitPotam” attack chain targeting Windows domains is another example of a technique that was recently assigned a CVE.) It’s a little puzzling why CVE-2021-42574 merited a “Critical” severity score, though. According to our calculations, this weakness should be more like a 5.6 on the CVSSv3 scale.

Should I be super scared?

It’s an interesting attack, and its universality is certainly attention-grabbing. With that said, there are some caveats to both novelty and exploitability. Attack techniques that leverage Unicode’s text expression aren’t new. The CVSS score assigned to this is overblown. To exploit this weakness, an attacker would need to have direct access to developers’ workstations, source code management system, or CI pipelines. If an attacker has direct access to your source code management system, frankly, you probably have bigger problems than this attack. Note that said “attacker” could be a legitimate, malicious insider; those types of attackers are notoriously difficult to fully defend against.

What should I do?

You should apply patches from vendors whose products you rely on just as you normally would, keeping in mind that because this flaw is present in so many tooling implementations, you could apply many patches and still be considered “vulnerable” in other implementations. The better thing to do would be to apply a fairly straightforward mitigation: Disallow BiDi directives in your code base if you’re writing in only English or only Arabic.

As noted above, you should absolutely heed the Unicode safety warnings (if available) in any source code repositories you use, and strongly consider using something like the aforementioned Red Hat Unicode directionality directive checker-script in source code control and continuous integration and deployment workflows.

We advise prioritizing truly critical patches and limiting service and system exposure before worrying about source code-level attacks that require local or physical access.

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.

PetitPotam: Novel Attack Chain Can Fully Compromise Windows Domains Running AD CS

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2021/08/03/petitpotam-novel-attack-chain-can-fully-compromise-windows-domains-running-ad-cs/

PetitPotam: Novel Attack Chain Can Fully Compromise Windows Domains Running AD CS

Late last month (July 2021), security researcher Topotam published a proof-of-concept (PoC) implementation of a novel NTLM relay attack christened “PetitPotam.” The technique used in the PoC allows a remote, unauthenticated attacker to completely take over a Windows domain with the Active Directory Certificate Service (AD CS) running — including domain controllers.

PetitPotam works by abusing Microsoft’s Encrypting File System Remote Protocol (MS-EFSRPC) to trick one Windows host into authenticating to another over LSARPC on TCP port 445. Successful exploitation means that the target server will perform NTLM authentication to an arbitrary server, allowing an attacker who is able to leverage the technique to do… pretty much anything they want with a Windows domain (e.g., deploy ransomware, create nefarious new group policies, and so on). The folks over at SANS ISC have a great write-up here.

According to Microsoft’s ADV210003 advisory, Windows users are potentially vulnerable to this attack if they are using Active Directory Certificate Services (AD CS) with any of the following services:

  • Certificate Authority Web Enrollment
  • Certificate Enrollment Web Service

NTLM relay attacks aren’t new — they’ve been around for decades. However, a few things make PetitPotam and its variants of higher interest than your more run-of-the-mill NTLM relay attack. As noted above, remote attackers don’t need credentials to make this thing work, but more importantly, there’s no user interaction required to coerce a target domain controller to authenticate to a threat actor’s server. Not only is this easier to do — it’s faster (though admittedly, well-known tools like Mimikatz are also extremely effective for gathering domain administrator-level service accounts). PetitPotam is the latest attack vector to underscore the fundamental fragility of the Active Directory privilege model.

Microsoft released an advisory with a series of updates in response to community concern about the attack — which, as they point out, is “a classic NTLM relay attack” that abuses intended functionality. Users concerned about the PetitPotam attack should review Microsoft’s guidance on mitigating NTLM relay attacks against Active Directory Certificate Services in KB500413. Since it looks like Microsoft will not issue an official fix for this vector, community researchers have added PetitPotam to a running list of “won’t fix” exploitable conditions in Microsoft products.

The PetitPotam PoC is already popular with red teams and community researchers. We expect that interest to increase as Black Hat brings further scrutiny to Active Directory Certificate Services attack surface area.

Mitigation Guidance

In general, to prevent NTLM relay attacks on networks with NTLM enabled, domain administrators should ensure that services that permit NTLM authentication make use of protections such as Extended Protection for Authentication (EPA) coupled with “Require SSL” for affected virtual sites, or signing features such as SMB signing. Implementing “Require SSL” is a critical step: Without it, EPA is ineffective.

As an NTLM relay attack, PetitPotam takes advantage of servers on which Active Directory Certificate Services (AD CS) is not configured with the protections mentioned above. Microsoft’s KB5005413: Mitigating NTLM Relay Attacks on Active Directory Certificate Services (AD CS) emphasizes that the primary mitigation for PetitPotam consists of three configuration changes (and an IIS restart). In addition to primary mitigations, Microsoft also recommends disabling NTLM authentication where possible, starting with domain controllers.

In this order, KB5005413 recommends:

  • Disabling NTLM Authentication on Windows domain controllers. Documentation on doing this can be found here.
  • Disabling NTLM on any AD CS Servers in your domain using the group policy Network security: Restrict NTLM: Incoming NTLM traffic. For step-by-step directions, see KB5005413.
  • Disabling NTLM for Internet Information Services (IIS) on AD CS Servers in your domain running the “Certificate Authority Web Enrollment” or “Certificate Enrollment Web Service” services.

While not included in Microsoft’s official guidance, community researchers have tested using NETSH RPC filtering to block PetitPotam attacks with apparent success. Rapid7 research teams have not verified this behavior, but it may be an option for blocking the attack vector without negatively impacting local EFS functionality.

Rapid7 Customers

We are investigating approaches for adding assessment capabilities to InsightVM and Nexpose to determine exposure to PetitPotam relay attacks.

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.