Letter To The European Commission About Age Verification And Social Networks

Post Syndicated from Bozho original https://techblog.bozho.net/letter-to-the-european-commission-about-age-verification-and-social-networks/

My previous post here in August was about the age verification plans of the European Commission. Since then the EC has proposed the EU KIDS Act, which implements the idea of age verification.

Yesterday I presented the alternative approach – heavily relying on parental control apps – on the OpenFest conference. Apart from proposing a local legislation in Bulgarian parliament, I’ve sent a letter the the European Commission. You can find it here. The text is as follows:


Dear President von der Leyen,
Dear Executive Vice-President Virkkunen,

Subject: The right approach to protecting children from the negative effects of social media

I’m writing this letter as a member of parliament from Bulgaria, as a former minister for digital transformation, as a technical expert and as a father.

Protecting children online has become a priority for the European Commission and for many EU governments, and rightly so. The threats online, the negative psychological effects of addictive designs and the algorithms that prioritize virality over quality have significant negative effects on children.

The European Commission has started addressing the addictive design problem, analyzes algorithmic bias and has undertaken an age verification initiative, in addition to long-term measures against CSAM, online crimes against children, etc.

While we all see the good intentions behind these initiatives, they sometimes lack the technical depth and the ambition to achieve swift results. My focus in this letter will be age verification, as the measure that is the most polarizing and may have significant negative side effects if done wrong. And I’m concerned that the currently selected approach by the European Commission is the wrong one.

The idea sounds simple – “social networks are proven to be detrimental to children’s mental health, and so they must not be allowed to use it. The way to do it is to add an age check before registration, so that only adults can use the service”. While simple to formulate, it’s much more difficult to implement, if not impossible.

There is an inherent paradox – if a solution is fully privacy-preserving, it’s ineffective. If it’s effective, it bears significant risks to privacy, as it will require every citizen to prove their identity online in order to use everyday services.

The European Commission has made a well-meaning attempt to design and implement a proper zero-knowledge proof of age. It’s a great tool, with proper cryptography, complex-yet-elegant. It has “just” one problem – it doesn’t account for the actual “threat actor” in this scenario – the user, who would try many things to circumvent the age limitation. As security consultant Paul Moore has brilliantly shown, you don’t have to compromise the age verification app in order to circumvent the flow – by a simple relay attack, where you just present someone else’s verified age credentials in order to use a service. The proof of concept was implemented as a chrome extension which relays age checks to 3rd party service, backed by an over-18 person’s device, which sends the proof to the service. That way a single adult can verify the accounts of all minors, and because of the necessary privacy guarantees, the relying party (the social network) won’t even know.

This is very likely to happen – “age verification as a service” providers will certainly pop-up to help minors get into social networks. What’s worse – some of these providers may collect children’s personal data, including phone number or social network account ID, in order to provide them with the much coveted proof of age. That data, purposefully or after an inevitable data breach, may be used by sex predators to target children. There are completely realistic nightmare scenarios, born from the good intention to limit the negative effects of social networks.

Even in a school context, a single over-18 (or over-16) student can lend their age verification app to help younger children register profiles. What are policy makers going to do then? Issue administrative fines for sharing age tokens/attestations? Criminalize it?

Any attempt to fix that technically, breaks the privacy guarantees; any attempt to fix it legally, is doomed to fail in enforcement.

My advice, in all my capacities listed in the beginning of this letter, is to abandon that approach and focus on a different approach – rely on parental control apps.

Parental control apps remain rudimentary, and perhaps there are reasons for this. They are not widely used and are often unintuitive and unreliable. However, they can be regulated and improved. They can also incorporate government-mandated lists of apps and domains restricted for children according to age. For example, a child protection agency could publish a list that parental control apps would be required to import automatically. Legislators could also require these apps to be pre-installed on every phone sold in their country. Parents would remain in control and could adjust the settings if they considered their children ready to use particular services responsibly.

Certain apps can be banned for under-14, others for under-16 and others – for under-18. Governments would have much better control over the exact services they deem risky for children, without the need for any changes on the service’s side. Or, if an app vendor wants to have it whitelisted, they may have to implement children-friendly versions.

Going further, this may eventually lead to platform-level parental control APIs, so that each app can read parental control settings, and on the other hand export parental control configuration options to be used in the parental control app.

What’s even better about this approach, is that VPNs can’t be used to circumvent it – it’s a device-level limitation, not service-level limitation, which needs to figure out the country of the user, which can only be done by their IP address.

And It’s completely privacy-preserving, as users don’t have to show or prove anything to anyone.
Of course, the harder part is making sure every child and parent has a parental control app installed. Information campaigns and teachers can help with that, and I’m sure it will achieve much better results than what we are seeing in Australia for example.
Even if the right age limitation measures are implemented, the efforts to limit the addictiveness and so-called “brainrot” on online platforms should continue.
We have proposed national legislation to implement the approach above. But in order to avoid fragmentation in the digital single market, and in order to have a working, cross-border model, where the experience of each country improves the model EU-wide, a solution should be discussed on a EU-level.

Yours sincerely,
Bozhidar Bozhanov,
Member of parliament of the Republic of Bulgaria

The post Letter To The European Commission About Age Verification And Social Networks appeared first on Bozho's tech blog.

AI Security

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2026/11/ai-security.html

Two weeks ago, I attended the [un]prompted AI security conference in San Francisco. It was an excellent event: three days of very dense talks about all aspects of AI security. (My talk was about integrous AI, and I will post it when it is online.)

AI security can be divided into three broad topics. It’s important for researchers to understand which one they are working on. And it’s important for us as a community to work on them all. They are: security of AI, security with AI, and security from AI. [un]prompted had good talks about all three.

Dell PowerEdge R770AP Review One Fast Intel Xeon 6 Server

Post Syndicated from Patrick Kennedy original https://www.servethehome.com/dell-poweredge-r770ap-review-one-fast-intel-xeon-6-server/

Today we are taking a look at Dell’s PowerEdge R770AP. The 2U server goes all-in on performance with a dual-socket Xeon 6 setup and 24 channels of DDR5 memory

The post Dell PowerEdge R770AP Review One Fast Intel Xeon 6 Server appeared first on ServeTheHome.

ASRock Rack DMRD16-2L+ Spotted with 16 DDR5 Slots for Diamond Rapids

Post Syndicated from John Lee original https://www.servethehome.com/asrock-rack-dmrd16-2l-plus-diamond-rapids-ocp-summit-2026/

We check out the ASRock Rack DMRD16-2L+ which is a 16-channel Intel Diamond Rapids Xeon motherboard with 128x PCIe Gen6 lanes over MCIO

The post ASRock Rack DMRD16-2L+ Spotted with 16 DDR5 Slots for Diamond Rapids appeared first on ServeTheHome.

Asahi Linux 7.3 progress report

Post Syndicated from corbet original https://lwn.net/Articles/1105936/

The Asahi Linux developers have put out a new report
on their progress toward a Linux distribution for Apple devices.

Some time ago, we were made aware of multiple attempts to exploit
our permissive licensing to hijack our work, with a direct view to
replacing the project and aggressively monetising Linux on Apple
Silicon. In some extreme cases, in-development feature code was
being lifted straight out of our personal forks and published
without attribution or lazily rewritten with LLM assistance to
obfuscate its origin. The MIT licence explicitly allows this, and
has no carveouts to protect against bad faith actors.

As such, we made the difficult decision to begin the process of
transitioning all of our repositories to the GNU General Public
License version 2 or later. Going forward all Asahi Linux code will
be licenced under strong copyleft licences only. Those who do not
learn from history are doomed to repeat it.

Amutable Foundations: A Technical Overview

Post Syndicated from corbet original https://lwn.net/Articles/1105934/

Lennart Poettering, Michael Vogt, and Joaquim Rocha have put together a
detailed overview
of what the Amutable Operating System (AOS) and
associated infrastructure will look like.

The image-based OS approach enables us to enforce some very strict
but powerful security properties, which elevate the security
posture of the system substantially above traditional Linux
systems. Specifically, let’s highlight seven major essential
security properties of AOS here:

  1. No Shell + No SSH + No Language Interpreters. By default AOS
    does not install a UNIX shell, nor makes remote access via SSH
    available on the nodes. Moreover, we do not install any of the usual
    language interpreters (Python, Perl, …) by default. For most nodes a
    shell or interpreted language support is not required and it removes a
    whole class of attacks.

  2. Signed Images Only. On AOS only images that come with Verity
    data signed by a signing key listed in the Verity keyring may be
    activated.

  3. […]

Седмицата (2–7 ноември)

Post Syndicated from Боряна Телбис original https://www.toest.bg/sedmitsata-2-7-noemvri/

Седмицата (2–7 ноември)

Целият свят ври и кипи. В Америка демократите пометоха републиканците на междинните избори, войните продължават, цените растат, политиците се обвиняват взаимно, а хората тук-там дори сменят мнението си.

У нас, слава богу, подобни сътресения няма. Всичко е подредено, стройно, вчесано. Всички са от една партия и навсякъде ще се ползва само един език, за да се разбираме точно и конкретно всички. На когото не му изнася, ще му показваме izhoda.

Седмицата (2–7 ноември)
Интернет фолклорът ни порасна с няколко века през последната седмица

Иначе изборите минаха, победителят е ясен, а България вече има първата жена, избрана за президент. Това самò по себе си е историческо постижение. Дали обаче е постижение и за правата на жените, е съвсем друг въпрос. В „Имаме си президентка. Съвсем“ Светла Енчева разглежда десетте години на Илияна Йотова в сянката на Румен Радев, отношението ѝ към равноправието и шансовете най-после да докаже политическата си самостоятелност.

Имаме си президентка. Съвсем

Светла Енчева коментира избора на първата жена президент на България. Йотова дължи възможността да заеме този пост на борбата за равноправие, но не е защитавала особено правата на жените. А след 10 години в сянката на Румен Радев тепърва ще трябва да доказва политическата си самостоятелност.

За това как Йотова стигна дотук и защо Андрей Гюров не успя да я спре, пише Емилия Милчева в анализа си на президентските избори. Накратко, оказа се, че изкуственото форсиране на страх от война е по-убедително от всеки реален опит за промяна. Особено когато успееш да убедиш избирателите, че опасността идва не от този, който води войната, а от онзи, който не иска да се оставят развързани ръцете на агресора.

Йотова ли спечели, или Гюров загуби?

На президентския балотаж страхът от война победи обещанието за промяна. Емилия Милчева анализира как управляващите превърнаха мира в предизборно оръжие, защо Андрей Гюров не успя да наложи собствен дневен ред и какво политическо бъдеще очаква двамата кандидати след изборите.

И понеже толкова много държим на мира, Александър Малинов реши да провери къде точно ще се скрием, ако този мир все пак ни подмине. В „Бомбоубежища за 1%“ става ясно, че с гражданската защита положението е доста по-неутешително, отколкото с предизборните обещания. Докато други европейски държави инвестират в убежища, системи за предупреждение и планове за действие при бедствия и военни конфликти, у нас защитените места стигат за по-малко от един процент от населението. Останалите явно ще разчитаме на мира, който ни обещаха.

Бомбоубежища за 1%

Внимание, внимание! Знаете ли къде трябва да се скриете при бедствие или военна атака? Не се притеснявайте, държавата също не знае съвсем. След изборите е време да поговорим и за по-съществени неща. Александър Малинов проверява имаме ли изобщо някакъв план и разказва как е в Европа.

Отвъд океана междувременно избирателите решиха да не разчитат повече на обещания. В брой 20 на „Гласовете на Америка“ Йоанна Елми разказва как демократите постигнаха най-голямата си изборна победа от десетилетия, какво не разбраха републиканците и защо реалните проблеми на хората се оказаха по-силни от поредната порция идеологически плашила.

Гласовете на Америка – брой 20

То бива, бива, ама чак пък това никой не го е очаквал. Демократите спечелиха убедително дори там, където доскоро изглеждаше немислимо, а републиканците имат доста поводи за размисъл. Йоанна Елми с обобщение на междинните избори в САЩ в 10 точки.

Но да оставим за момент естествения интелект, който ни управлява, и да видим какво става с изкуствения, защото и той се бори за своето място под слънцето, така да се каже. Илия Тошев задава един стар въпрос в нова обстановка: „Кой пази пазачите?“ Когато ИИ агентите вече могат да кандидатстват за кредити, да вземат решения и да действат от наше име, кой контролира тях и кой контролира онези, които имат правото да ги спират?

Илия предлага конкретни правила за независим надзор, публичност и възможност за обжалване. Когато този, който определя правилата, сам контролира и спазването им, надзорът лесно се превръща във формалност. В България имаме достатъчно опит с подобни сбъркани модели, макар и без участието на изкуствен интелект, и би трябвало да сме наясно. Оу, уейт… както се казва по новия законопроект.

Кой пази пазачите?

Да оставиш ИИ да ти намери кредит звучи удобно. Но какво става, ако нещо се обърка, и към кого се обръщаш тогава? Илия Тошев ни превежда през практическата страна на живота с ИИ: кой отговаря за агентите, които действат от наше име, и как да защитим интересите си, когато вече решават вместо нас.

И докато се чудим колко власт да дадем на машините, все по-рядко си задаваме въпроса какво ни отнемат те. В разговора си със Стефан Иванов аржентинската писателка Саманта Швеблин обяснява защо литературата е противоположност на радикализацията, защо машините ни правят предвидими и скучни и какво губим, когато престанем да мислим с хора, които мислят различно от нас. Много хубав разговор, особено в страна, в която очевидно сме решили да се разбираме само на един език, буквално и преносно.

Саманта Швеблин: Да избягаме от езика, за да докоснем тялото на читателя

Преди броени дни станалата вече култова аржентинска писателка Саманта Швеблин в дискусия с Георги Господинов и Дария Карапеткова разказа за рисковете и радостите да четеш, пишеш и мислиш света през литературата днес. Часове преди това тя се срещна и със Стефан Иванов – ето техния разговор.

Тази седмица Зорница Христова ни предлага две книги за трудното изкуство да живееш с друг човек. В „По буквите: Линч, Рой“ тя представя „Отвъд морето“ на Пол Линч и „Моят подслон и моята буря“ на Арундати Рой. В едната двама мъже са заседнали в лодка насред океана, в другата майка и дъщеря цял живот се опитват да намерят правилната дистанция помежду си. И в двете се оказва, че за да оцелееш заедно с някого, се изисква повече от това да го накараш да мисли като теб.

По буквите: Линч, Рой

Тази седмица Зорница Христова поставя на фокус две чудесни съвременни книги, в които апокалипсисът е „в една лодка“ близки хора, но изплуването се оказва невъзможно без широтата на разбирането и приемането, без щедростта на протегнатата сурова и помилваща ръка.

За да продължаваме да публикуваме текстове, в които не всички мислят еднакво, имаме нужда от вашата подкрепа. „Тоест“ се издържа от читателите си. За щастие, независимата журналистика струва доста по-малко от една предизборна кампания, но все пак не може да се прави съвсем без пари. Ако харесвате това, което четете, подкрепете ни. Обещаваме да не ви казваме на какъв език да мислите и откъде да излизате, освен ако, разбира се, не търсите izhoda ot cqloto tova bezobrazie.

Приятна почивка!

Friday Squid Blogging: New Jurassic Squid Predecessors

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2026/11/friday-squid-blogging-new-jurassic-squid-predecessors.html

News story: “Scientists discover a bizarre Jurassic ‘squid’ unlike anything ever seen.”

Scientists have identified the “fattest” belemnite ever discovered, a bizarre, barrel-shaped squid relative that lived in Wyoming’s ancient seas 160 million years ago. The exceptionally rare fossils reveal a creature unlike anything previously known, potentially a predator of smaller squid-like animals and a surprising survivor of a supposedly vanished family.

As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.

Blog moderation policy.

Addressing protocol security gaps in multi-tenant Kubernetes

Post Syndicated from Ajinkya Patil original https://aws.amazon.com/blogs/security/addressing-protocol-security-gaps-in-multi-tenant-kubernetes/

Protocols like Android Debug Bridge (ADB) and Web Real-Time Communication (WebRTC), by default, use unencrypted channels for network communications and don’t support enterprise authentication mechanisms like JSON Web Tokens (JWTs). In a multi-tenant Kubernetes cluster—including Amazon Elastic Kubernetes Service (Amazon EKS)—pods can reach other tenants’ open ports by default unless you configure network policies to restrict cross-namespace traffic. Also, modifying each protocol individually doesn’t scale. This post describes an architecture built on three reusable components: namespace-scoped mutual TLS (mTLS) gateways, managed TURN relay through Amazon Kinesis Video Streams, and JWT identity chains tied to an enterprise identity provider (IdP). The post focuses on architecture decisions and learnings rather than step-by-step deployment.

This post assumes an EKS cluster with namespace isolation configured, an enterprise IdP that issues JWTs, and AWS Private Certificate Authority (AWS Private CA)—a managed service for issuing private certificates—set up in your account. cert-manager—an open-source Kubernetes add-on that automates certificate issuance and renewal—and the AWS Private CA issuer plugin should already be running in the cluster. The architecture also assumes permissions to deploy Envoy Gateway, a Kubernetes API gateway built on the Envoy proxy. The key authentication mechanism used is mTLS, where both client and server present certificates to verify each other.

The challenge: Unauthenticated protocols in multi-tenant Kubernetes

ADB, a command-line tool for communicating with Android devices, requires a proxy or custom API to handle authentication; its unencrypted channel exposes data in transit. Virtual Network Computing (VNC), a protocol for remote desktop access, and similar TCP services share this problem: their credentials are local to the protocol, with no path to a central identity store.

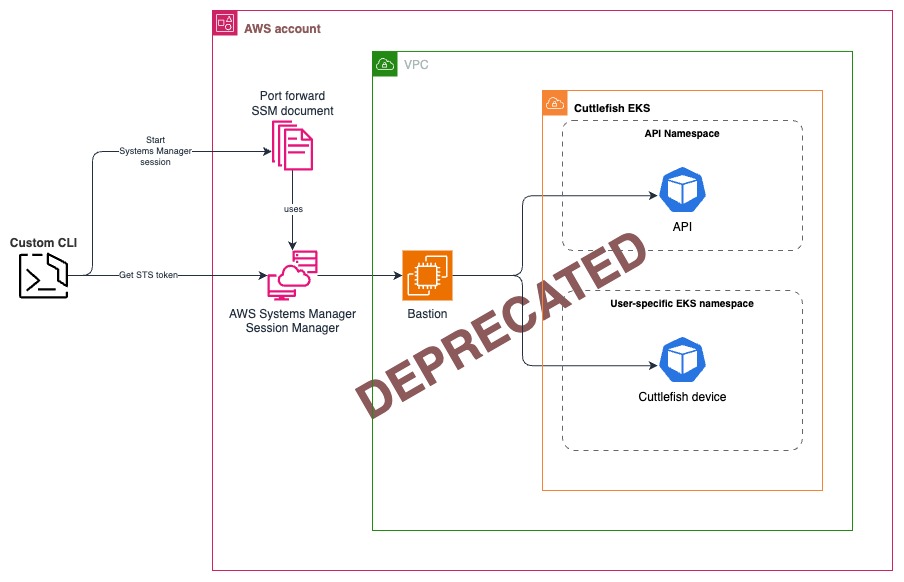
In the Cuttlefish deployment (Cuttlefish is Google’s configurable virtual Android device that runs in containers), the first approach routed this traffic through a bastion host to the Amazon EKS control plane, as Figure 1 shows.

Figure 1: Previous architecture (superseded), shown for comparison only. Communication flow between developer workstation, bastion host, and Amazon EKS control plane

Figure 1: Previous architecture (superseded), shown for comparison only. Communication flow between developer workstation, bastion host, and Amazon EKS control plane

Figure 1 shows a common pattern across the industry to access a private Amazon EKS cluster. We share it to help others identify and migrate away from similar designs for low latency environments. Do not implement this design. The current architecture is described and shown later in this post.

In the now deprecated architecture, a custom API handles authentication by checking each user’s identity against the enterprise IdP and enforcing pod-level authorization. The custom API powers a command-line interface (CLI) that lets you list pods in your assigned namespace and connect to your devices.

The JWT identity chain maps each user to an AWS Security Token Service (AWS STS) RoleSessionName, so every AWS API call in the audit log traces back to a specific person, even in a multi-tenant environment.

Those credentials set up a two-hop port forward that goes from your machine to the bastion, then from the bastion to the target pod. Because all traffic was routed through the Kubernetes API server, concurrent sessions created a throughput bottleneck even though the cluster itself stayed private.

Why self-managed relay infrastructure falls short

A TURN server—a media relay—is needed when communicating parties are behind a NAT Gateway and can’t set up direct peer-to-peer connections.

The initial deployment used STUNner, an open source Kubernetes Session Traversal Utilities for NAT (STUN) and Traversal Using Relays around NAT (TURN) gateway designed for WebRTC media ingestion. STUNner introduced three operational and security challenges.

Because STUNner had no native integration with AWS services or the enterprise IdP, we built a custom token-exchange service to convert IdP tokens into time-limited, namespace-scoped TURN credentials. As usage grew, patching, monitoring, and scaling the TURN servers became a recurring burden. Pod migrations between Availability Zones required manually updating routing rules, and STUNner dropped WebRTC connections during peak usage.

WebRTC’s signaling server introduced a separate security risk. WebRTC encrypts media using Datagram Transport Layer Security (DTLS) and Secure Real-Time Transport Protocol (SRTP) but doesn’t define authentication or encryption for the signaling server; you must build that yourself, which leaves control-plane signaling exposed.

The architecture doesn’t use the Kinesis Video Streams signaling channel because integrating it required substantial changes to the Cuttlefish source patch. The Cuttlefish source code was patched to support non-Google TURN servers, and further changes to support non-Google signaling servers deviated the deployment further from upstream Cuttlefish, risking compatibility issues. Instead, the architecture kept the default Cuttlefish signaling server, with JWT-based session validation and TLS termination at the signaling endpoint designed around it at the application layer.

Namespace-scoped mTLS gateways and managed media relay

The architecture retains namespace isolation, JWT-based authentication, the custom authorization API, and the Cuttlefish patch; the last three of which are custom to this deployment. All components except Cuttlefish patch are reusable.

The reusable components include namespace-scoped Envoy Gateway for mTLS-authenticated TCP proxying, cert-manager-driven certificate rotation through AWS Private CA, and Kinesis Video Streams as a managed TURN provider.

The mTLS gateway assumes several other controls are already in place:

  • Default-deny NetworkPolicy in each tenant namespace. Without this, traffic can bypass the gateway.
  • JWT-based authentication through the custom API. The API validates each user’s identity against the enterprise IdP before returning connection details.
  • Namespace-scoped mTLS certificates issued by AWS Private CA through cert-manager.
  • Kubernetes namespace isolation with scoped role-based access control (RBAC).

ADB connectivity through mTLS

For ADB connectivity, the architecture uses mTLS authentication with Envoy Gateway. Each namespace runs its own Envoy Gateway instance, which routes traffic only to pods within that namespace. cert-manager, running in the cluster with the AWS Private CA issuer plugin, requests short-lived mTLS certificates from AWS Private CA for each namespace at creation time. In production, apply NetworkPolicies before deploying the gateway and issuing certificates.

The certificate commonName uses the convention <user-namespace>.eks.internal so that Envoy can validate the certificate against the expected namespace during the mTLS handshake. The .eks.internal suffix is a naming convention for internal cluster certificates; choose a domain that doesn’t conflict with your organization’s DNS. The usages field specifies both client authentication and server authentication because the same certificate authenticates the client to the gateway and the gateway to the client during the mutual TLS exchange. A cluster-scoped AWSPCAClusterIssuer is used instead of a namespace-scoped AWSPCAIssuer so that a single CA configuration can issue certificates across all tenant namespaces without duplicating issuer resources in each one.

Before deploying Envoy Gateway, each tenant namespace needs a NetworkPolicy that enforces a default-deny ingress posture.

Each certificate is issued with a 12-hour lifetime. A shorter lifetime means a compromised certificate expires quickly without requiring Certificate Revocation List (CRL) or Online Certificate Status Protocol (OCSP) infrastructure, while the 4-hour renewal window gives cert-manager multiple retry attempts before expiry. cert-manager tracks expiry and re-requests a new certificate from AWS Private CA before the current one lapses (by default, renewal starts at the two-thirds mark of the certificate’s lifetime). Envoy Gateway picks up the renewed certificate through Kubernetes Secrets using its Secret Discovery Service (SDS), with no pod restart required.

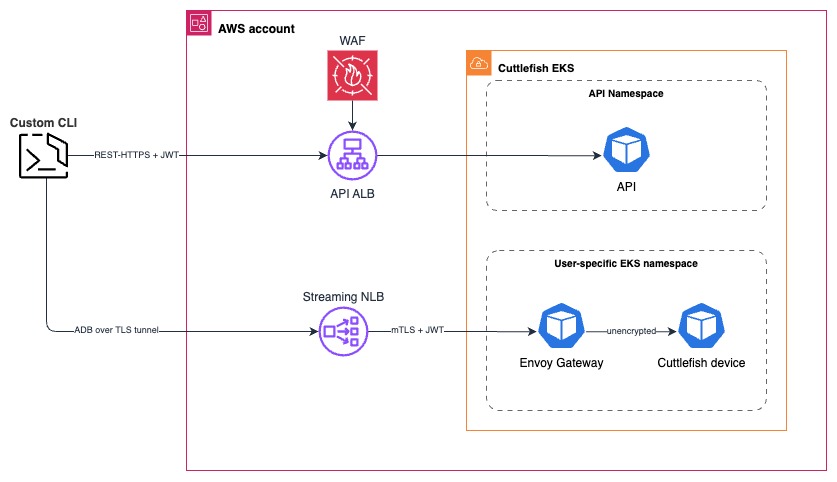
You first authenticate with the enterprise IdP through the custom CLI, which calls the custom API. The API validates your JWT, confirms your namespace assignment, and returns connection details for the appropriate namespace-scoped Envoy Gateway, including the client certificate for that namespace. The API delivers the certificate over HTTPS. Because certificates are namespace-scoped and expire in 12 hours, a compromised response yields access only to the holder’s own namespace for a limited window. The CLI then presents this certificate to establish a direct mTLS connection, through Envoy, to the target pod. The JWT proves who you are, and the mTLS certificate proves which namespace the connection belongs to.

Envoy proxies the TCP stream directly to the pod and pools connections to reduce latency. The hop between Envoy and the pod isn’t encrypted by mTLS. NetworkPolicy restricts ingress so that only the namespace-scoped Envoy Gateway can reach the ADB port on the target pod. For environments with compliance requirements, extend mTLS to the pod using a sidecar proxy or pod-level certificates. Evaluate this gap against your organization’s data classification and regulatory requirements.

For the REST API path, the custom API sits behind AWS WAF. The ADB data path has no WAF protection; it relies on mTLS, NetworkPolicies, and namespace isolation.

Figure 2: ADB communication flow using Envoy Gateway and custom REST API

Figure 2: ADB communication flow using Envoy Gateway and custom REST API

Figure 2 shows this ADB communication flow using Envoy Gateway and the custom REST API. It logs your authenticated identity, namespace, and timestamp. The mTLS certificate doesn’t carry a user identifier in its subject field. This applies when namespaces are strictly 1:1 with users. For shared namespaces or regulated environments requiring granular attribution, issue per-user certificates from AWS Private CA.

WebRTC relay through Kinesis Video Streams

Kinesis Video Streams provides built-in STUN and TURN infrastructure and signaling channels. It replaced the self-managed STUNner because it integrates with AWS Identity and Access Management (IAM), so the custom token-exchange service is no longer needed. This is an important factor in reducing operational costs. For implementation details, see the Amazon Kinesis Video Streams WebRTC developer guide, which covers signaling channel setup, IAM policies, and TURN credential retrieval.

Kinesis Video Streams WebRTC charges per active signaling channel, per signaling message, and per TURN streaming minute. Idle namespaces incur no TURN cost. See Amazon Kinesis Video Streams pricing for latest pricing and Amazon Kinesis Video Streams with WebRTC service quotas for service quotas.

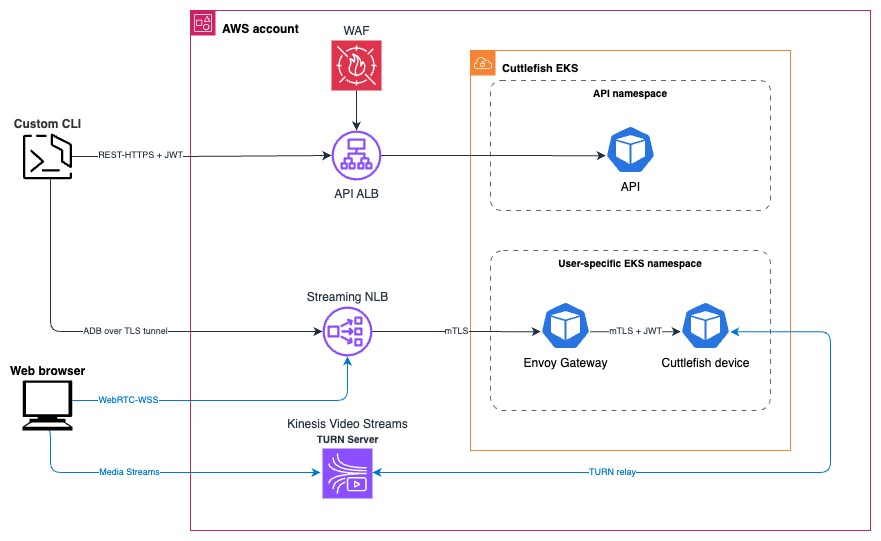
Figure 3: Final architecture with ADB and WebRTC communication channels

Figure 3: Final architecture with ADB and WebRTC communication channels

Figure 3 shows both ADB and WebRTC communication channels in the completed architecture. Each path has different controls: ADB traffic flows through the namespace-scoped Envoy Gateway, where mTLS and NetworkPolicies enforce access. WebRTC media relay runs through Kinesis Video Streams, with IAM scoping credentials per session. The custom REST API is the only HTTP-based path; it runs over HTTPS with AWS WAF at the edge.

The JWT identity chain connects all three paths: the custom API validates each user’s identity before any connection opens, so the audit log records who connected to which namespace and when.

Applying this pattern to other unauthenticated protocols

The mTLS gateway and certificate rotation pieces transfer directly to most TCP protocols. The TURN relay is specific to WebRTC and similar media-streaming protocols that need NAT traversal. The JWT identity chain requires custom work and isn’t directly transferable. You need to build the API that validates tokens and maps users to namespaces, and a client that retrieves and presents the certificate. The Cuttlefish source patch is specific to this case study and not reusable.

Two common protocol families show how the reusable parts apply:

  • VNC and RDP both store credentials locally, with no path to an enterprise identity provider. Wrapping VNC in mTLS through Envoy replaces the shared password model with certificate-based identity. RDP benefits similarly: certificate authentication works without domain-joining the containers, so you don’t need Active Directory inside each one.
  • MQTT, SIP, and similar TCP protocols often encrypt the payload but skip session-level authentication entirely; meaning you can verify what was sent but not who sent it. Wrapping these protocols in mTLS through Envoy closes that gap without modifying the protocol itself.

JWT identity chain secures session establishment at the application layer. For Internet of Things (IoT) device management, industrial control, or game streaming, Envoy Gateway adds mTLS to TCP protocols that lack built-in encryption in transit. Managed TURN through Kinesis Video Streams handles NAT traversal for WebRTC-based streaming components.

Performance results

Application installs through the dual port-forwarding chain (local machine to bastion, bastion to pod) took 3–4 minutes, and individual ADB commands took 1–2 seconds per round trip.

After migrating to the mTLS Envoy Gateway, ADB commands added under 50 ms of gateway latency compared to local setup. The latency was measured as the difference in round-trip time between a command sent through Envoy and one sent to a local Android device. Through Envoy, individual ADB commands completed in under 100 ms and application installs finished in under 30 seconds, because Envoy proxies the TCP stream directly to the pod instead of routing through the Kubernetes API server. This was an improvement from 1–2 seconds for ADB commands and 3–4 minutes for application installs using bastion host setup.

Key implementation lessons

The main concern addressed by replacing bastion-host forwarding with mTLS proxying was latency compared to local setup. Gateway overhead stayed under 50 ms and met developer expectations.

After migrating to Kinesis Video Streams, WebRTC connections stayed stable during peak usage, and pod migrations between Availability Zones no longer required manual updates to routing rules. Because Kinesis Video Streams integrates with IAM, new protocols added to the cluster are automatically covered by the same audit trail with no additional logging configuration needed.

Security considerations

mTLS authenticates both ends of a connection and encrypts traffic in transit, but it only works when other controls are in place. The NetworkPolicy and pod security controls described in the preceding ADB connectivity section must be in place before mTLS adds value. Without default-deny ingress rules, traffic bypasses the gateway entirely. At the application layer, the custom API validates each user’s JWT before issuing connection details and logs the identity, namespace, and timestamp for every session. Certificates expire after 12 hours and cert-manager rotates them automatically. Short-lived certificates reduce exposure, but if your threat model requires immediate revocation, you need CRL or OCSP infrastructure on top of AWS Private CA. Envoy Gateway is a trust boundary. Review its configuration, resource limits, and access controls against the Envoy security best practices.

The custom API is the primary trust boundary in this architecture. Apply the same rigor to its security review, logging, and access controls as you would to any authentication service.

Conclusion

With namespace-scoped mTLS gateways and managed TURN relay, you can secure unauthenticated protocols on shared EKS clusters without modifying the protocols themselves. ADB command latency drops from 1–2 seconds to under 50 ms, and WebRTC connections remain stable during pod migrations. See the Envoy Gateway documentation, cert-manager documentation, and Amazon Kinesis Video Streams WebRTC developer guide to build and deploy this architecture.

If you have questions about this post, contact AWS Support or start a new thread on AWS re:Post.
Ajinkya Patil

Ajinkya Patil

Ajinkya is a Senior Security Consultant at Amazon Professional Services, specializing in security consulting for AWS customers across the automotive, finance, and media industries since 2019. He has presented at AWS re:inforce and contributed articles to the AWS Security Blog and AWS Prescriptive Guidance. Outside of work, he enjoys traveling and photography.

The collective thoughts of the interwebz