Post Syndicated from turnoff.us original http://turnoff.us/geek/linux-shutdown-2024/
Post Syndicated from turnoff.us original http://turnoff.us/geek/linux-shutdown-2024/
Post Syndicated from Juan Carlos Alvarez original https://www.servethehome.com/using-crucial-pro-ddr5-6000-32gb-2x-16gb-dimms-micron/
We take the Crucial Pro DDR5-6000 32GB kit (2x 16GB DIMMs) for a spin since they support both Intel XMP and AMD EXPO
The post Using Crucial Pro DDR5-6000 32GB 2x 16GB DIMMs appeared first on ServeTheHome.
Post Syndicated from LastWeekTonight original https://www.youtube.com/watch?v=G-dJMqpGvjM
Post Syndicated from xkcd.com original https://xkcd.com/2902/
Post Syndicated from corbet original https://lwn.net/Articles/964337/
The 6.8-rc7 kernel prepatch is out for
testing.
So we finally have a week where things have calmed down, and in
fact 6.8-rc7 is smaller than usual at this point in time. So if
that keeps up (but that’s a fairly notable “if”) I won’t feel like
I need to do an rc8 this release after all.So no guarantees, but assuming no bad surprises, we’ll have the
final 6.8 next weekend.
Post Syndicated from turnoff.us original http://turnoff.us/geek/minimum-viable-elevator/
Post Syndicated from Grant Bourzikas original https://blog.cloudflare.com/welcome-to-security-week-2024
April 2024 will mark my one-year anniversary as the Chief Security Officer at Cloudflare. In the past year, we’ve seen a rapid increase in sophisticated threats and incidents globally. Boards and executives are applying significant pressure to security organizations to prevent security breaches while maintaining only slight increases to budgets. Adding regulatory scrutiny, global security leaders are under pressure to deliver on the expectations from executives to protect their company. While this has been the expectation for over 20 years, we have recently seen a significant rise in attacks, including the largest and most sophisticated DDoS attacks, and the continued supply chain incidents from Solarwinds to Okta. Along with more nation state sponsored attackers, it is clear security professionals – including Cloudflare – can’t let their guards down and become complacent when it comes to security.
This past year, I met with over a hundred customers at events like our Cloudflare Connect conference in London, Chicago, Sydney, and NYC. I spoke with executives, policy experts, and world leaders at Davos. And I’ve been in constant dialogue with security peers across tech and beyond. There is much consistency amongst all security leaders on the pain points and concerns of Chief Information Security Officers (CISOs), spanning every geography and industry, from startups to large Fortune 500s.
Over the course of this week we will announce new products inspired by these conversations that respond to common challenges faced by CISOs around the world. We will cover many aspects of these security concerns, ranging from application security to securing employees and cloud infrastructure. We will also be sharing stories of how we do things at Cloudflare, and some thought leadership blog posts.
As a CSO for more than 20 years for some of the world’s largest and most complex companies, I was drawn to the rapid innovation, unique market position and the global network that Cloudflare offers. Looking back on my first year at Cloudflare, the discussions I have had with customers has shaped me into a better CSO. Sharing my own challenges and listening to others has expanded my own understanding of the complex issues that we, Cloudflare, can learn from and adopt.
The core pillars of my organization are to Protect Cloudflare, Foster Innovation, and share “How Cloudflare does it.” My team is customer zero: first to use Cloudflare products and collaborate on needs of security organizations. Innovation weeks are certainly a key feature of the Cloudflare way, and I’m extremely proud to be able to open Security Week 2024 by announcing a series of exciting new products and features.
There are three key challenges that have emerged in my discussions with CISOs and security practitioners: responding to risks and opportunities from AI, maintaining visibility and control as cloud technology changes so quickly, and how to consolidate technologies to effectively manage the security and IT budget.
One of the key topics I heard at Davos is how global leaders can address urgent global issues. As a society, we are facing a number of challenges, ranging from the environment to the ongoing effort to keep democracies functioning. The role of the Internet has never been more crucial, and I believe it’s a shared responsibility to keep it functioning and improve its security.
Our product and engineering teams have been working to deliver an array of solutions aligned to these challenges, and ultimately helping build a better Internet.
No surprise, AI is the number one topic of discussion. At Davos, AI was the common theme across all industries, with a core concern of how to secure and protect our investments. As a leader in AI inference, our engineering and product teams have been working hard on building a way to protect our own, and our customers’, AI models and applications.
This week our product teams are announcing tools to safeguard applications in the era of AI as well as AI-powered features helping our customers simplify how they interact with our analytics.
As a CSO, securing data is a core capability that is only made more challenging as the workforce may choose to use open AI services without understanding the risks. We have some announcements this week aligned with preventing data leakage from AI, as well as how you can use AI to secure against AI-enhanced phishing.
Finally, we will also share our philosophy of how AI can be used to increase the level of defense and security against increasingly sophisticated attacks.
Effective security programs keenly focus on reducing complexity, increasing visibility, and robust alerting capabilities. A resounding message of 2024 is security by design, rather than bolted-on security. Security by design sounds easy but is more challenging for those of us without a greenfield.
While most do not have the luxury of starting over, many are succeeding by eliminating legacy tooling, such as third party storage tools, and at the same time gaining visibility and control.
There are new ways to secure and connect multi-cloud environments with consistent policy management. Our team will be sharing many new releases they are working on, and a recent acquisition, all aligned to this challenge we all face.
Every year security leaders are asked to do more with less. With economic uncertainty persisting into 2024, budget constraints have each of us critically analyzing our security stack for value and simplicity. Everyone is looking for strategies that not only reduce costs, but reduce complexity and increase your posture by removing room for human error. The CISOs who I see succeed in this environment have built programs based on simplification. Cloud migrations and zero trust architecture implementations have many asking if those transformations delivered on the promise of simplification and scale. My own zero trust journeys have given me a deep appreciation for the Cloudflare approach in moving away from expensive and complex security architectures.
2024 will be a pivotal year for the Internet. Geopolitical conflict and the elections around the world are being heavily analyzed for impact across every industry. This week we will share how we can leverage our robust platforms to stand by our mission to help build a better Internet and protect global democracy and large scale international events.
Innovation weeks are a great tradition at Cloudflare. This is where we launch new capabilities and share new ways to solve the challenges we have heard from our customers. No surprise, Security Week will be my personal favorite. I hope you each walk away with something that makes your job just a little easier.
Post Syndicated from digiblurDIY original https://www.youtube.com/watch?v=I6wwCL7gMVo
Post Syndicated from corbet original https://lwn.net/Articles/964305/
The
6.7.8 and
6.6.20
stable kernel updates have been released. They contain a single patch
addressing an ntfs3 filesystem build error introduced in the previous
round of updates.
Post Syndicated from Juan Carlos Alvarez original https://www.servethehome.com/gowin-semi-fanless-1u-25gbe-appliance-is-so-close-intel-nvidia/
We show the GoWin semi-fanless 1U 25GbE appliance prototype to show what is possible at the edge of the Intel Core i3-N305’s capabilities
The post GoWin Semi-Fanless 1U 25GbE Appliance is So Close appeared first on ServeTheHome.
Post Syndicated from Explosm.net original https://explosm.net/comics/predators
New Cyanide and Happiness Comic
Post Syndicated from Oglaf! -- Comics. Often dirty. original https://www.oglaf.com/better-angels/


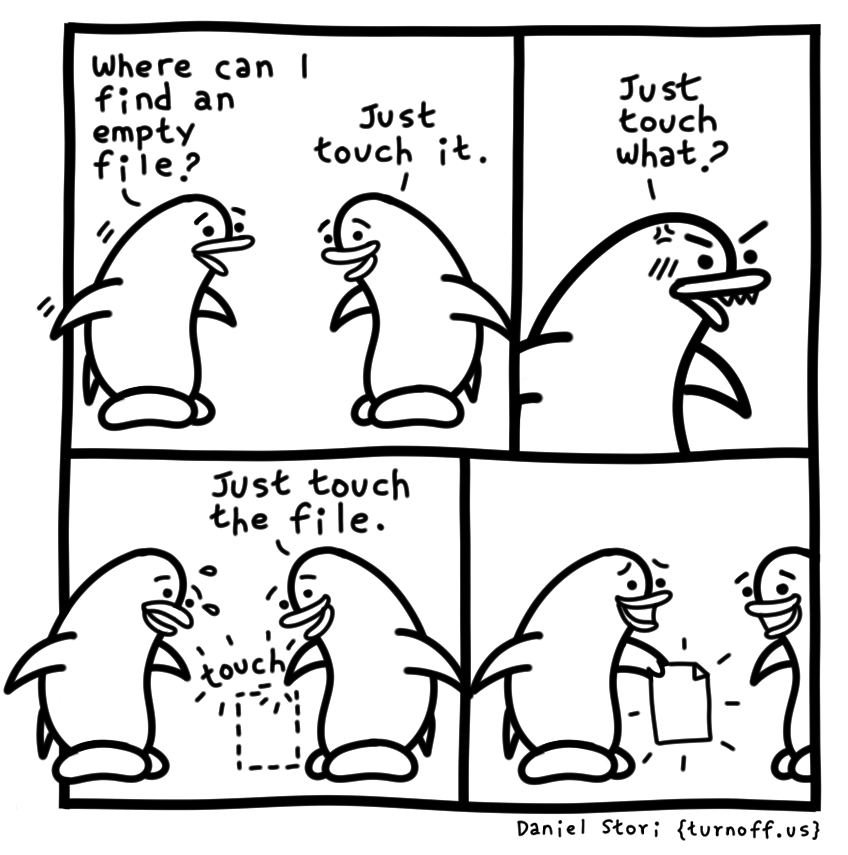
Post Syndicated from turnoff.us original http://turnoff.us/geek/just-touch-it/
Post Syndicated from Techmoan original https://www.youtube.com/watch?v=QVc0n0_WrXw
Post Syndicated from Боряна Телбис original https://www.toest.bg/sedmitsata-26-fevruari-2-mart/

Преди 47 години човечеството е успяло да създаде машина, която толкова да го обича, че да се обърне и да му направи една последна снимка от Космоса, преди да изключи камерата за всичко останало завинаги. Става въпрос за космическата сонда „Вояджър 1“, която днес се намира на ръба на Слънчевата система, в безкрайното нищо, на милиарди километри от нас. Освен това леко се е побъркала и данните, които изпраща, са абсолютно неразчетими, но никой не я хули за това. Защото този необичаен пътешественик свърши много повече работа и стигна много по-далече, отколкото изобщо някой някога си е представял. През 1990 г. именно „Вояджър 1“ ни оставя онази прословута снимка на малката синя точка, която изглежда като изгорял пиксел на черен екран. Днес космическите телескопи ни пращат къде-къде по-детайлни изображения, но нищо не може да се сравни с бледосинята пясъчна люспа, която „Вояджър 1“ ни показа за последно. На нея е всичко.
Вече втора седмица поред в „Тоест“ се вълнуваме какво става и какво ще стане с „Вояджър 1“, защото краят на сондата ще бъде и краят на цяла епоха. Миналата седмица за това ни разказа Михаил Ангелов в своите научни новини, а сега публикуваме една изключително емоционална и също толкова информативна статия за „Вояджър 1“, която вкарва по симпатичен начин в исторически контекст целия разказ около изстрелването на сондата и ни подръчква да си позволим да сме малко по-чувствителни и сантиментални, което ние, разбира се, избягваме да правим просто защото няма време за всичко. Статията е на Дъг Мюър, публикуваме я с неговото специално разрешение, а преводът е на Анелия Костова.
Обираме леко патоса и преместваме погледа си от далечния Космос към твърде близката и натопорчена политическа реалност, която на фона на вечността изглежда крайно несъществено. Но понеже предстои така напоително обговаряната ротация, се налага да кажем няколко думи и за нея. Прави го Емилия Милчева в текста си „Осми март, ден първи“, като задава правилните въпроси:
кога и как ще бъде скрепен документално съюзът – ще бъдат ли заложени реформи на основни системи, или ще се ограничат до механизма за назначения, изобщо ще се стигне ли до кооперативно равновесие, от което (и) обществото да има известни ползи?
Дали сглобката ще премине в по-стабилен строеж, предстои да разберем. Междувременно тунел „Железница“ на автомагистрала „Струма“ премина от строителен обект в годна за експлоатация инфраструктурна единица. Оказа се обаче, че самите ние като нация може би не сме съвсем преминали в настоящия век, защото продължаваме да живеем като едни предмодерни българи, които вграждат икони в тунели и невести в мостове, за да сме по-сигурни в стабилността на самото съоръжение. По този въпрос разсъждава в текста си „Икони вместо работещи институции“ Светла Енчева.
От потенциалните външни разпади на мостове, тунели и сглобки минаваме към едни много по-важни и много по-крехки – вътрешните разпади на душата на малки уязвими в самотата си съставни части. На тях е посветена тазседмичната рецензия на Антония Апостолова. Книгата на фокус в рубриката „На второ четене“ е сборникът с разкази „Академия за китове“ от Виолета Златарева, в която се разказва за хората с нестандартна психика и за миговете, в които не са съвсем себе си.
В една Малайзия с лют сос и съкровища ви предлагаме да се оттеглим като за финал на тазседмичния „Тоест“. Това е първата част от пътеписа на Петя Кокудева за живописната азиатска страна, където покрай пътищата растат помело, манго, драконов плод и ананас, макаци могат да ти откраднат телефона само защото го мислят за храна, а ако ти самият искаш нещо да закусиш, съвсем спокойно може да го направиш с един лют ориз.
Приятно четене на новия „Тоест“.
Post Syndicated from Rohit Kumar original https://www.servethehome.com/supermicro-aoc-a25g-i2sm-25gbe-nic-review-intel-e810-xxvam2/
In our Supermicro AOC-A25G-i2SM review, we see how this dual 25GbE SFP28 NIC performs based on the Intel E810-XXVAM2 controller
The post Supermicro AOC-A25G-i2SM 25GbE NIC Review Intel E810-XXVAM2 appeared first on ServeTheHome.
Post Syndicated from Explosm.net original https://explosm.net/comics/predator
New Cyanide and Happiness Comic
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/03/friday-squid-blogging-new-extinct-species-of-vampire-squid-discovered.html
Paleontologists have discovered a 183-million-year-old species of vampire squid.
Prior research suggests that the vampyromorph lived in the shallows off an island that once existed in what is now the heart of the European mainland. The research team believes that the remarkable degree of preservation of this squid is due to unique conditions at the moment of the creature’s death. Water at the bottom of the sea where it ventured would have been poorly oxygenated, causing the creature to suffocate. In addition to killing the squid, it would have prevented other creatures from feeding on its remains, allowing it to become buried in the seafloor, wholly intact.
Research paper.
As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.
Read my blog posting guidelines here.
Post Syndicated from Donnie Prakoso original https://aws.amazon.com/blogs/aws/mistral-ai-models-now-available-on-amazon-bedrock/
Last week, we announced that Mistral AI models are coming to Amazon Bedrock. In that post, we elaborated on a few reasons why Mistral AI models may be a good fit for you. Mistral AI offers a balance of cost and performance, fast inference speed, transparency and trust, and is accessible to a wide range of users.
Today, we’re excited to announce the availability of two high-performing Mistral AI models, Mistral 7B and Mixtral 8x7B, on Amazon Bedrock. Mistral AI is the 7th foundation model provider offering cutting-edge models in Amazon Bedrock, joining other leading AI companies like AI21 Labs, Anthropic, Cohere, Meta, Stability AI, and Amazon. This integration provides you the flexibility to choose optimal high-performing foundation models in Amazon Bedrock.
Mistral 7B is the first foundation model from Mistral AI, supporting English text generation tasks with natural coding capabilities. It is optimized for low latency with a low memory requirement and high throughput for its size. Mixtral 8x7B is a popular, high-quality, sparse Mixture-of-Experts (MoE) model, that is ideal for text summarization, question and answering, text classification, text completion, and code generation.
Here’s a quick look at Mistral AI models on Amazon Bedrock:

Getting Started with Mistral AI Models
To get started with Mistral AI models in Amazon Bedrock, first you need to get access to the models. On the Amazon Bedrock console, select Model access, and then select Manage model access. Next, select Mistral AI models, and then select Request model access.

Once you have the access to selected Mistral AI models, you can test the models with your prompts using Chat or Text in the Playgrounds section.

Programmatically Interact with Mistral AI Models
You can also use AWS Command Line Interface (CLI) and AWS Software Development Kit (SDK) to make various calls using Amazon Bedrock APIs. Following, is a sample code in Python that interacts with Amazon Bedrock Runtime APIs with AWS SDK:
import boto3
import json

bedrock = boto3.client(service_name="bedrock-runtime")

prompt = "<s>[INST] INSERT YOUR PROMPT HERE [/INST]"

body = json.dumps({
    "prompt": prompt,
    "max_tokens": 512,
    "top_p": 0.8,
    "temperature": 0.5,
})

modelId = "mistral.mistral-7b-instruct-v0:2"

accept = "application/json"
contentType = "application/json"

response = bedrock.invoke_model(
    body=body,
    modelId=modelId,
    accept=accept,
    contentType=contentType
)

print(json.loads(response.get('body').read()))
Mistral AI models in action
By integrating your application with AWS SDK to invoke Mistral AI models using Amazon Bedrock, you can unlock possibilities to implement various use cases. Here are a few of my personal favorite use cases using Mistral AI models with sample prompts. You can see more examples on Prompting Capabilities from the Mistral AI documentation page.
Text summarization — Mistral AI models extract the essence from lengthy articles so you quickly grasp key ideas and core messaging.
You are a summarization system. In clear and concise language, provide three short summaries in bullet points of the following essay.

# Essay:
{insert essay text here}
Personalization — The core AI capabilities of understanding language, reasoning, and learning, allow Mistral AI models to personalize answers with more human-quality text. The accuracy, explanation capabilities, and versatility of Mistral AI models make them useful at personalization tasks, because they can deliver content that aligns closely with individual users.
You are a mortgage lender customer service bot, and your task is to create personalized email responses to address customer questions. Answer the customer's inquiry using the provided facts below. Ensure that your response is clear, concise, and directly addresses the customer's question. Address the customer in a friendly and professional manner. Sign the email with "Lender Customer Support."

# Facts
<INSERT FACTS AND INFORMATION HERE>

# Email
{insert customer email here}
Code completion — Mistral AI models have an exceptional understanding of natural language and code-related tasks, which is essential for projects that need to juggle computer code and regular language. Mistral AI models can help generate code snippets, suggest bug fixes, and optimize existing code, accelerating your development process.
[INST] You are a code assistant. Your task is to generate a 5 valid JSON object based on the following properties:
name:
lastname:
address:
Just generate the JSON object without explanations:
[/INST]
Things You Have to Know
Here are few additional information for you:
Now Available
Mistral AI models are available today in Amazon Bedrock, and we can’t wait to see what you’re going to build. Get yourself started by visiting Mistral AI on Amazon Bedrock.
Happy building,
— Donnie
Post Syndicated from Christophe De La Fuente original https://blog.rapid7.com/2024/03/01/metasploit-weekly-wrap-up-03-01-2024/
This week, our very own sfewer-r7 added a new exploit module that leverages an authentication bypass vulnerability in ConnectWise ScreenConnect to achieve remote code execution. This vulnerability, CVE-2024-1709, affects all versions of ConnectWise ScreenConnect up to and including 23.9.7.The module creates a new administrator user account on the server, which is used it to upload a malicious extension (.ashx file) and get code execution as the NT AUTHORITY\SYSTEM user on Windows or root user on Linux, depending on the target platform.
Authors: WatchTowr and sfewer-r7
Type: Exploit
Pull request: #18870 contributed by sfewer-r7
Path: multi/http/connectwise_screenconnect_rce_cve_2024_1709
Description: This PR adds an unauthenticated RCE exploit for ConnectWise ScreenConnect (CVE-2024-1709).
features command.auxiliary/admin/kerberos/inspect_ticket module with improved error messages and support for printing Kerberos PAC credential information.ldap_esc_vulnerable_cert_finder and ldap_query were also updated to improve usability.help command to visually align command names to the same width to improve readability.CreateSession option to be available for payloads that did not make sense.auxiliary/capture/ldap module’s handling of NTLM hashes.You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro