Post Syndicated from The Atlantic original https://www.youtube.com/shorts/xHZ41WCc8eM
Bargain Z Mount lens
Post Syndicated from Matt Granger original https://www.youtube.com/shorts/ZNwhJo_yQwk
Final release for the 7.2 stable series
Post Syndicated from jzb original https://lwn.net/Articles/1104629/
Greg Kroah-Hartman has announced the release of the
7.2.15 kernel, with a handful of updates.
Note, this is the LAST 7.2.y kernel release. After this one the 7.2.y kernel
tree is end-of-life. Please move to 7.3.y at this time.And yes, you aren’t imagining things, this one went “end-of-life” a bit sooner
than normal. But based on the release cycle at the moment, and the number of
pending cc: stable patches in the queue, I figured it was better this way so we
can focus on the latest 7.3.y release as it would require us to keep 8
different branches alive at the same moment, a taxing task under the best of
times.
“Social Change is Really Hard” || David Brooks and Sam Moyn on radicalism and moderation
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=R39V_-uXzjo
NVIDIA Updates Rubin GPU Specs as First Production Hardware Arrives
Post Syndicated from Ryan Smith original https://www.servethehome.com/nvidia-updates-rubin-gpu-specs-as-first-production-hardware-arrives/
As production hardware starts shipping, NVIDIA has updated some of the specifications for its Rubin GPU platforms
The post NVIDIA Updates Rubin GPU Specs as First Production Hardware Arrives appeared first on ServeTheHome.
Spangles
Post Syndicated from Oglaf! -- Comics. Often dirty. original https://www.oglaf.com/spangles/
A massive pile of security updates for Saturday
Post Syndicated from corbet original https://lwn.net/Articles/1104612/
Security updates have been issued by AlmaLinux (.NET 10.0, .NET 11.0, .NET 8.0, .NET 9.0, aspell, bind, bind9.18, container-tools:1.0, container-tools:rhel8, curl, dogtag-pki, ignition, java-21-openjdk, python-pillow, tomcat, and virt:rhel, virt-devel:rhel), Debian (antiword, cyrus-sasl2, dovecot, dpdk, nss, python-git, and thunderbird), Fedora (7zip, aegisub, aom, apptainer, arm-none-eabi-binutils-cs, assimp, avr-binutils, baresip, barman, bind9-next, btrfs-backup-ng, chezmoi, chromium, cifs-utils, clevis-pin-trustee, composer, containerd, curl, docker-buildx, dotnet10.0, evolution, evolution-data-server, evolution-ews, exim, fips-provider, firefox, flare-im, forgejo, freeipa, freerdp, gcc, gegl04, ghostscript, GitPython, glib-networking, gnome-shell-extension-gsconnect, golang-x-mobile, hcloud, helix, httpd, ImageMagick, iperf3, jfrog-cli, jupyterlab, keepassxc, kernel, knot-resolver, krb5, kryoptic, libdigidocpp, libheif, libindi, libinstpatch, libpng12, libpng15, librabbitmq, libre, libXi, libzip, linux-firmware, Lmod, log4net, markdownlint-cli2, mingw-freetype, mingw-gstreamer1, mingw-gstreamer1-plugins-bad-free, mingw-gstreamer1-plugins-base, mingw-gstreamer1-plugins-good, mingw-libpng, mingw-LibRaw, mingw-python-certifi, mingw-python3, mongo-c-driver, mstflint, mutt, nant, nebula, nix, nsd, ntpsec, openbao, openjpeg, openssl3, openvpn, perl-Badger, perl-CLI-Simple, perl-Cpanel-JSON-XS, perl-CSS-Inliner, perl-Encoding-FixLatin, perl-ExtUtils-Typemaps-Default, perl-GD-SecurityImage, perl-HTML-Query, perl-libnet, perl-Markdown-Render, perl-Net-IDN-Encode, perl-Net-Whois-Raw, perl-Plack, perl-Plack-Middleware-ReverseProxy, perl-Text-CSV_XS, pgbouncer, php-getid3, php-pecl-mongodb2, python-boto3, python-botocore, python-cairosvg, python-django5, python-django6, python-jupyter-builder, python-mkdocs-rss-plugin, python-nbdime, python-nh3, python-notebook, python-pydantic-core, python-pypdf, python-uv-build, python3.10, python3.11, python3.12, python3.13, python3.14, qdigidoc, qdl, qt5-qtbase, radicale, rclone, rt, ruff, rust-ammonia, rust-archive-trait, rust-astral-html, rust-astral-ini, rust-astral-mail-headers, rust-astral-pubgrub, rust-astral-version-ranges, rust-astral_async_http_range_reader, rust-astral_async_zip, rust-asyncband, rust-backtrace, rust-blake2b_simd, rust-blake3, rust-cargo-semver-checks, rust-chrono, rust-clap-cargo, rust-constant_time_eq, rust-dua-cli, rust-faster-hex, rust-gengo-bin, rust-gitui, rust-lzma-rust2, rust-object, rust-object0.37, rust-object0.38, rust-object0.39, rust-onefetch, rust-ppmd-rust, rust-quick-junit, rust-rbw, rust-regorus, rust-reqsign, rust-reqsign-aliyun-oss, rust-reqsign-aws-core, rust-reqsign-aws-v4, rust-reqsign-aws-v4a, rust-reqsign-azure-storage, rust-reqsign-command-execute-tokio, rust-reqsign-core, rust-reqsign-file-read-tokio, rust-reqsign-google, rust-reqsign-http-send-reqwest, rust-reqsign-huaweicloud-obs, rust-reqsign-oracle, rust-reqsign-tencent-cos, rust-reqsign-volcengine-tos, rust-routinator, rust-rustls, rust-ruzstd, rust-sccache, rust-tar-codec, rust-tar-framing, rust-tokei, rust-totp-rs, rust-trustfall-rustdoc-adapter, rust-trustfall-rustdoc-adapter57, rust-trustfall-rustdoc-adapter60, rust-typed-path, rust-zip, rust-zip0.6, rust-zip2, rustup, samba, SDL3_image, socat, stargz-snapshotter, stgit, sudo, syncthing, thunderbird, tor, trafficserver, ty, unbound, unshield, uv, webkitgtk, wordpress, xorg-x11-server, xorg-x11-server-Xwayland, zchunk, and zvbi), Mageia (libgit2), Red Hat (go-toolset:rhel8 and rhc), SUSE (ab-av1, ansible-core, aws-nitro-enclaves-cli, bouncycastle, cadvisor, chromium, cifs-utils, coredns, crun, dr_libs-devel-20260901, dssim, epiphany, expat, forgejo, freetype2-devel, fuseiso-20260614, gh, ghostscript, gosec, gvfs, hashcat, hauler, hugo, ImageMagick, kernel-devel, kubevirt1.9, libmikmod, libsoup, percona-toolkit, perl-cpanel-json-xs, perl-dancer2-plugin-auth-extensible, perl-mozilla-ca, pocketbase, putty, python-brotli, python-CairoSVG, python-cairosvg, python-django, python-pypdf, python-urllib3_1, roundcubemail, rsyslog, shadowsocks-rust, shadowsocks-libev, stgit, suseconnect-ng, tailscale, trivy, and vlc), and Ubuntu (brotli).
How We Could Have Backdoored Bash (Hacktron blog)
Post Syndicated from corbet original https://lwn.net/Articles/1104262/
The Hacktron blog documents how
the group was able to compromise the GNU Savannah forge and could have
pushed malware into any of the projects hosted there.
Using Hacktron, we found that an email address like
`touch${IFS}/tmp/savane-rce-proof`@attacker.example gave any
registered user code execution on its backend. From there, we made
our account a superuser, impersonated Bash’s maintainer, and
confirmed we could add an SSH key with push access to the upstream
Bash repository. An unpatched kernel gave us root access and access
to a GNU backup server. We reported it to the FSF on May 11, 2026.
America’s Most Useless Congress Faces the Midterms | The David Frum Show
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=7wr0hnOAUIo
The District Where Gerrymandering May Backfire on the GOP
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/OTsjHSW6Mno
$150 vs $4,000 Flashes! Does Price Matter in 2026?
Post Syndicated from Matt Granger original https://www.youtube.com/watch?v=pwHPB3CC-wU
A History of Ghosts (Revised.)
Post Syndicated from The History Guy: History Deserves to Be Remembered original https://www.youtube.com/watch?v=jGhk-wrJuy4
Rediffusion Reditune’s BGM for the 1960s…and beyond.
Post Syndicated from Techmoan original https://www.youtube.com/watch?v=be8ML8G7oKI
The Issues That Could Affect the Hispanic Vote
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/-Hsx1nZf-3Q
Intel Q3 2026 Earnings Data Center Soars While PC Faces Memory Pressure
Post Syndicated from Cliff Robinson original https://www.servethehome.com/intel-q3-2026-earnings-data-center-foundry-client/
Intel’s Q3 2026 earnings highlighted how well the data center segment is doing and how rough the client segment is due to DRAM and NAND pricing
The post Intel Q3 2026 Earnings Data Center Soars While PC Faces Memory Pressure appeared first on ServeTheHome.
Седмицата (26-31 октомври)
Post Syndicated from Светла Енчева original https://www.toest.bg/sedmitsata-26-31-oktomvri/
Размишлявате ли, скъпи читатели на „Тоест“? Или вече сте решили дали и за кого да гласувате? Иска ми се в неделя всички да сме будни. Не само защото е Денят на народните будители, а защото от избора, който направим в този ден, зависи в каква посока ще върви България. А ако на първия тур по изключение нямаше контролиран вот, сега залозите са вдигнати и може да очакваме гласуване по команда на някои места. Арестуваните кметове от ДПС на Белица и Сунгурларе бяха пуснати под домашен арест в четвъртък. Положението е – сделка или да.
В четвъртък беше и дългоочакваният дебат между Илияна Йотова и Андрей Гюров. За всички, за които истината има значение, екипи на „Дойче Веле“, „Клуб Z“ и Factckeck.bg (може да пропускам някоя медия) са си направили труда да извършат проверка на фактите. С естествените си интелекти, не с ИИ. А от „Дойче Веле“ дори са посочили кой е авторът и кой – редакторът на текста за всяко от проверените твърдения. Сред авторите е и Емилия Милчева.
Но ако Емилия, на чиято енергия се възхищавам неблагородно, е проверявала факти в четвъртък до късна доба, това не означава, че е оставила „Тоест“ без обичайната си петъчна статия. Напротив. Покрай всичките си ангажименти тя е успяла дори да създаде и запише документалната поредица в Storytel „Без име“, посветена на темата за насилствената асимилация на мюсюлманите в България. Ето новия ѝ коментар за „Тоест“ „Властта отвори три фронта за победа“. Ала ако отсега издам кои са тези три фронта, може и да не прочетете статията, така че ще мълча като партизанка.
Властта отвори три фронта за една победа
Може нито един от двамата кандидати да не ни кара да тичаме към урните в неделя. Но гласуването не е въпрос на вдъхновение, а на усилието да не подариш избора си на някой друг. Емилия Милчева пише за залога на този избор и за трите фронта, на които властта работи за победата на Йотова.
Като казах „партизанка“, ей такива асоциации от времето на социализма се завръщат в съзнанието ми, като наблюдавам новата власт. След като последната ми статия беше готова, в Mediapool излезе публикация, която, за съжаление, вече нямаше как да включа в текста си. В нея се проследява как от началото на войната на Русия срещу Украйна до септември 2026 г. БТА (чийто директор днес е кандидат-вицепрезидент) около 700 пъти цитира руската държавна информационна агенция ТАСС, както и „РИА Новости“, която е под санкциите на ЕС. БТА се позовава на ТАСС дори когато става дума за събития в ЕС и САЩ, отразени от информационните агенции на съответните държави. Няма да се учудя, ако прогресивните ни управляващи възстановят и практиката отпреди 10 ноември всеки петък централната информационна емисия да е съветската (пардон – руската), а след нея да ни се пуска руски филм.
Кой иска какѝ форевър*?
Между двата тура на президентските избори залогът е по-голям от това кой ще влезе на „Дондуков“ 2. „Прогресивна България“ вече има пълната власт, а през последните месеци показва и как я използва. Светла Енчева коментира сливането на партия и държава, в което някои от нас вече са живели.
Не че американците са цъфнали и вързали. Но следващата седмица са междинните избори, резултатите от които може да доведат до известно ограничаване на безконтролната власт на Тръмп. Лично аз съм любопитна да разбера как ще се представи кандидатът за сенатор на демократите в Тексас Джеймс Таларико. Ако спечели, това ще е знак, че е възможно връзката между християнството и политиката и да не е за сметка на демократичните ценности.
В новия брой на бюлетина си „Гласовете на Америка“ Йоанна Елми прави разбор на ситуацията в САЩ в навечерието на междинните избори. Управлението на Тръмп е затънало в корупция и недоверие, рейтингът му пада, но пък опозицията в лицето на демократите няма единна идея за какво се бори, тоест каква е алтернативата.
Гласовете на Америка – брой 19
Америка отива на междинни избори със скъп живот, републиканци с пълни каси и демократи, които още се чудят каква партия искат да имат. В новия брой на бюлетина ни за САЩ Йоанна Елми гледа отвъд изборната аритметика – към залозите за следващите две години.
Изводът е: да внимаваме какво си пожелаваме. Тодор Колев пееше „Как ще ги стигнем американците“, но стана така, че май те ни стигнаха. И то не в хубавото.
Този път, по който е поела България, не изглежда добре, погледнат от Брюксел, става ясно от статията на Анахит Хачикян „За София, Брюксел и трептенето на пеперудите“. Както потрепването на крилата на пеперуда в Китай може да е свързано с ураган на другия край на света, така България не е изолирана от света. И действията и бездействията на управляващите имат последствия и отвъд страната. А те не са приятни.
За София, Брюксел и трептенето на пеперудите
Афинитетът на Румен Радев към „мултивекторна политика“ води дотам, че България пада от два воюващи стола на земята. Поне така изглеждат нещата в Европейския парламент, разказва ни Анахит Хачикян. Румен Радев е недоволен от ЕП, но познава ли изобщо механизмите на европейските институции?
Изобщо, страх да го хване човек. С което директно скачаме в стихотворението на месеца. Този път то е на Ина Иванова. Може би някои от вас я познават само като говорещата с тези хора, но Ина е преди всичко майстор на думите.
*** Така се е свил в черупката си моят мъничък страх
Така се е свил в черупката си моят мъничък страх, така подло кове отвътре с неточните удари на наточените си юмручета, да не останеш на себе си-в себе си да не влезеш твърде навътре-насаме гледай никога да не оставаш-никъде, особено там, където като шипки просветват, като капчица
Докато Ина дефилира при нас с поезията си, Роси Михова, която също разговаря с интересни хора, призовавайки призраците на други интересни хора, този път ни дарява с интервю с Мариус Куркински със специалното съдействие на Елизабет Лойд и Оскар Уайлд. Бихте ли пропуснали такъв балсам за душата?
Мариус Куркински: Любовта ни е такава – театрална и трагична
Този път Роси Михова разтваря пред очите ни не просто анкета, а същински викториански „албум за признания“. Въпросите ги задават Елизабет Лойд и Оскар Уайлд. Отговаря Мариус Куркински. Роси изящно медиира този (почти) спиритичен сеанс.
А където призраци, там и вампири. В навечерието на Хелоуин Екатерина Петрова ни разкрива не дневниците, а речниците на вампира. Етимологии пътуват през векове, държави и езици като едни неуловими вампири, на които не можеш им хвана спатиите.
Речниците на вампира
Езикът не е херметически затворен съд, защото в противен случай лесно би се превърнал в тенджера под налягане. За пореден път Екатерина Петрова го доказва с историята на думи, свързани с празника Вси светии. Излиза, че преди да „внесем“ Хелоуин, сме „изнесли“ ключови негови съставки.
Настана време и за обичайната ми препоръка. Този път тя е простичка – да гласувате. Да изберете себе си – бъдещето, което желаете за себе си и за обичните си хора, средата, в която искате да живеете.
Разбира се, винаги препоръчвам да подкрепите и нас, ако искате да има „Тоест“. В „Тоест“ трудът – авторски, редакторски, коректорски – се заплаща по достойнство. Но в резултат не сме на червено само в месеците, през които сме работили по-малко или изобщо не сме работили, както може да се уверите и от финансовия ни отчет. А не искаме да е така. Надявам се, че и вие не искате.
За финал ще почеша любопитството ви. Очаква се възраждането на нещо, на което аудиторията на „Тоест“ много ще се зарадва. Но няма пък да ви кажа какво е то. Ще ви държа в напрежение.
Friday Squid Blogging: Bigfin Squid Off California Coast
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2026/10/friday-squid-blogging-bigfin-squid-off-california-coast.html
Neat video:
The sighting, announced September 2, marks the first time anyone has spotted a live bigfin squid, which belongs to the Magnapinna genus, in the northeastern Pacific Ocean.
As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.
[$] Removing binder.c
Post Syndicated from daroc original https://lwn.net/Articles/1102982/
The final talk at Kangrejos 2026 was about the removal of the C implementation
of Android’s
Binder driver, the primary interprocess communication mechanism
used on Android devices. Carlos Llamas announced that he had deleted the C
code to general applause, and then shared some insights about what went into
replacing the C implementation. Alice Ryhl, who has worked on the Rust
implementation for some years, added her own thoughts about what the most
difficult and interesting parts of the transition were.
4 real? Tracking exploitation and patching of eMudhra’s weak keys
Post Syndicated from Maxime Guerreiro original https://blog.cloudflare.com/emudhra-patching/
On October 19, 2026, we learned about eMudhra’s eight shockingly weak keys: where eMudhra was trusted to pick a 115-digit number for their virtual combination lock protecting the Internet, they picked the number 4. Not even four digits, just the number 4. The other seven keys were similarly weak: 56, 66, 115, 155, 156, 230 and 237.
The next day, we wrote a blog post on the immediate action we took to mitigate this leak, and what customers needed to do on their end to stay secure. Now, we are sharing a more in-depth follow up on the evidence we’ve seen of exploitation, and the progress seen on visitors patching their systems.
Let's start with the scale of the problem. A certificate authority (CA) with weak keys this serious is unprecedented, and the potential consequences are significant. While there have been plenty of compromised certification authorities in the past (such as DigiNotar, TÜRKTRUST, and TrustWave), access to their keys has always been contained to a degree; these incidents gave a limited set of attackers or organizations the ability to issue fraudulent certificates. The eMudhra incident is fundamentally different; the affected intermediate private keys could be recovered almost instantly by anyone from the public certificates themselves. Anyone can independently recover these same signing keys and create certificates for any domain that an unpatched client not enforcing Certificate Transparency would accept.
eMudhra announced they’re exiting the public CA business and have claimed a mistake in a key generation script, but have not yet shared the script. They signed a certificate revocation list (CRL) with what might’ve been a correctly generated key, and subsequently corrected it to be signed with the weak key.
How did that come to be and why didn’t that set off alarms? Much has to be cleared up, including the role of the auditors and cross signers. This blog proposes the fixes and next steps for organizations to ensure they are secure.
Patching Cloudflare
Our primary concern remains the security impact on Cloudflare, our customers, and the Internet as a whole. At the time of writing, all high priority Cloudflare systems have been patched. A small number of confirmed low impact tickets is being worked on.
We started patching high-impact systems immediately on October 19. These included customer origin-facing proxies using Pingora, responsible for most of our outbound connections. These were patched in hours to reject the vulnerable eMudhra keys. At the same time, we started an AI-assisted analysis of our source code to find all other systems that trust these weak keys. Within four hours we had a full analysis. We assigned a ticket with preliminary analysis for each system, and asked the team to confirm and/or adjust the analysis before the end of the day. Where high impact was identified, we asked to patch immediately, and for the lower impact, remediation was due at the end of last week.
Has Cloudflare seen exploitation across its network?
To track whenever a customer’s server (or attacker) presents a certificate signed by eMudhra’s weak keys, we added logging to Pingora. As this outbound service accounts for the vast majority of outgoing TLS connections from a Cloudflare machine, any attacker attempting to snoop using the eMudhra keys would trigger this logging. The logging finished rolling out October 21.
At the time of writing, a week later, we’ve seen about 22,000 attempted handshakes with the weak eMudhra keys. Two-thirds of the attempts were fetches of test sites such as emudhra.we-have-a-problem.com (which we mentioned in the developer guidance in our earlier post). Almost all of the remaining third went to origins who appeared to set up a certificate for themselves using the weak intermediate. Every handshake configured to verify the certificate was refused, as we already patched.
About 160 of these handshakes stood out: the certificates’ Subject Alternative Names (SANs) were naming other organizations’ domains, unrelated to the Server Name Indication (SNI) requested in the handshake. Some of those names were domains related to consumer IoT devices. We noticed as well that those forged certificates were made after the keys leaked and some were valid for over two years, longer than any public CA may issue. However, these certificates looked like the servers' own default certificates rather than part of an attempt to intercept our connections. They named domains other than the ones being connected to, so they would have failed hostname verification anyway. And in several cases, a server presented the same certificate to connections from many of our locations, which means it came from the server itself rather than from something on a single network path.
Thus while there is no evidence of the weak keys being used to intercept Cloudflare's connections so far, these keys appear to have been used to forge certificates within hours of the weakness becoming public: one of the forged certificates we saw was dated October 20 at 18:19 UTC, less than an hour after Mozilla's bug report was made public. This does not exclude carefully targeted interception. For that we have to rely on the usual indirect signals of system compromise — and so far, we have not seen any such signals.
How many visitors are still vulnerable?
So much about patching Cloudflare, but what about our visitors? We cannot directly test whether a visitor still trusts the weak keys without breaking connections, so we have to do something more indirect. For that we used our challenge pages:
We rolled out an update to send out two probe connections on a fraction of challenge pages: one probe to ca1.cloudflarecaptcha.com and one to ca2.cloudflarecaptcha.com. Initially we installed an eMudhra signed certificate on ca1.cloudflarecaptcha.com and a regularly signed certificate on ca2.cloudflarecaptcha.com as control. Then we record whether these probes succeeded. This allows us to see if visitors that are served a challenge page still trust the weak eMudhra keys.
What did we find? With 50 million probes over the last week, we see this:
Big caveat upfront: by design the traffic to these challenge pages is highly skewed. There are many (unconfirmed) bots in there. Also, only clients that execute JavaScript (like browsers) will send probes.
The jump in the data is due to the following changes—all times are UTC:
- October 23 15:30, we changed our control endpoint to also serve an eMudhra certificate, but this time without signed certificate timestamps (SCTs). There were some differences in acceptance, but not large. We could’ve added a new endpoint, but that would’ve required a slow release of our challenge platform. Changing the endpoint was easier.
- October 23 16:30, our challenge platform rolled back to a previous version because of an unrelated issue. The probes returned October 27 at 10:00.
- October 27 16:37, we noticed we did not send the G3 cross-sign, which not all clients knew about, and added it to both endpoints. We removed SCTs from both.
- October 27 16:49, we switched ca2 to chain up to the AAA Certificate Services root.
- October 27 18:18, we ramped up probes to be included from 1% to 10% of all challenge pages served on non-paying customer zones.
With those caveats out of the way: what do we notice? Up-to-date modern browsers are mostly patched, but bots and old browsers are not. Also embedded browsers, like Android WebView, lag behind patching with 30–40% still accepting. Over the first weekend (with the monitoring gap), we see clear evidence of patching, but afterwards we see little movement.
On October 29 around 18:00 UTC, we released a detection that caught a large influx of bot traffic identifying as Chrome 150-154 on macOS. This can look like patching in the top graph, but it is actually a change in traffic classification: the same user agents show a corresponding increase in acceptance among traffic with bot signals detected in the bottom graph.
Chrome 150-154 on Linux is the notable exception: its acceptance continues to decline, consistent with further patching in that cohort. Given the bot-heavy and changing traffic mix, that evidence is suggestive rather than conclusive. Otherwise, we still see little movement.
Breaking down by network (ASN) we see:
Across the large networks, more than half of probes still accept the compromised chain, both among traffic with no bot signals detected (top graph) and traffic with bot signals detected (bottom graph). Over the weekend we saw some patching, but afterwards the trend has been flat.
The big caveat still holds: traffic is skewed by (unconfirmed) bots. But bots are also just software that need security updates. And if they’re in any way representative of overall software updates, then the picture is quite dire indeed.
What can you do?
Patch! Dennis Jackson has a great crowdsourced website with instructions. Especially if you’re a developer on macOS, you want to follow these instructions. If you’re a Cloudflare customer, check out last week’s blog post on what needs to be done on your end when using certain products like WARP or Tunnel.
Looking ahead
At Cloudflare, we have a quick-revocation mechanism in place in some products. To bring it to more systems at Cloudflare and industry, we’re excited about projects like upki that understand a trust store can’t be a static list of root certificate authorities, but needs the ability to be quickly updated with information like revocation and certificate transparency keys. As vulnerabilities are discovered at a faster pace than ever, it is vital that they can be addressed quickly and effectively.
Implement least-privilege access with designations in Amazon SageMaker Unified Studio
Post Syndicated from Priyanka Chaudhary original https://aws.amazon.com/blogs/big-data/implement-least-privilege-access-with-designations-in-amazon-sagemaker-unified-studio/
When teams move data and AI work to production in a shared environment, one question quickly becomes unavoidable: who can do what? Amazon SageMaker Unified Studio now answers it with designations, which are named permission sets that give administrators granular control over the actions each member can perform within a project. Administrators define a designation once, then assign it to project members. A member might sign in through an AWS Identity and Access Management (IAM) role, an IAM user, or an AWS IAM Identity Center user or group. In each case, designations help you give each persona only the access its responsibilities require. Effective access also depends on identity and resource policies, service control policies, permissions boundaries, group memberships, and how the customer configures permission sets and assignments. Designations integrate with AWS CloudFormation, and there is no additional charge to use them beyond Amazon SageMaker Unified Studio itself.
In this post, we walk through why differentiated permissions matter, how designations work, and how to create and assign your first designation using the console and the AWS Command Line Interface (AWS CLI).
The challenge: One project, many roles
A single SageMaker Unified Studio project often brings together data engineers, data stewards, analysts, and machine learning (ML) engineers, each needing very different access. Consider a financial services team running its Lakehouse and ML workflows in one project. Engineers build and schedule extract, transform, and load (ETL) pipelines, and a steward approves subscription requests to keep sensitive data governed. Analysts query curated tables for dashboards, and ML engineers iterate on models in notebooks. They all work on the same data, but their access needs differ. The steward shouldn’t alter production pipelines, analysts shouldn’t launch expensive compute, and the scheduled ETL service account shouldn’t share permissions with someone running exploratory experiments. In the past, common approaches included giving everyone the same broad project role or splitting the work across separate projects.
“We automated everything about how teams get set up in SageMaker Unified Studio. Projects are created, members are synced from our directory daily, and data sources are registered without anyone clicking a button. The one thing we couldn’t automate was controlling what each person could do once they were inside. Solution teams, data scientists, and business analysts all arrived with the same access. With designations, we now define each user type’s permissions as part of the same automation that creates the project, so the right access is enforced from day one.”
— Tim Kopacz, Cloud Platform Architect, Swiss Life Germany
Without a purpose-built mechanism to scope permissions within a project, organizations face operational risk. A user might accidentally delete a connection that disrupts a production workload or modify catalog settings outside their area of responsibility. Teams often work around this by creating a separate project for each persona to isolate access. That approach fragments data across project boundaries and adds provisioning and member-management overhead. As more teams onboard, these workarounds compound to slow adoption and increase the governance burden.
Designations address several common scenarios:
- Controlling access to Notebooks: Grant members full access, read-only access, or no access to notebooks within a project, so compute-intensive interactive work is available only to the roles responsible for it. This helps control costs by limiting who can run notebook workloads.
- Separating exploration from production: Grant exploratory users read and explore access while production service accounts run scheduled workflows, all within the same project.
- Supporting governance workflows: Assign specific personas responsibility for data stewardship, subscription approval, and metadata management, which helps prevent other members from bypassing your review process.
How designations work
Designations separate policy definition from member assignment, which is what makes them reusable across projects.
- Define once: A domain administrator creates a designation by selecting granular permissions. For example, publish an asset, create data products, or approve subscriptions. Permissions are grouped into categories such as Catalog, Project, Subscriptions, Connections, and Notebooks, and are backed by the Cedar policy language.
- Assign per project: Within a project, the project owner assigns one designation to each member. When a member performs an action through the portal or the API, SageMaker Unified Studio evaluates the assigned designation. It permits or denies the action based on the permissions the designation contains. Additionally, a member can also inherit designations through single sign-on (SSO) group membership. If a user is directly assigned one designation and also belongs to a group assigned to another, the user receives the union of both permission sets. Because effective permissions are the union of direct and group-inherited designations, review SSO group assignments regularly so members don’t receive more access than intended.
Because a designation is defined once and assigned per project, you get consistent permissions across every project without recreating policies each time. Data engineers, stewards, analysts, and automated pipelines can work within the same project with different permissions, which keeps data unified in one place rather than fragmented across duplicate projects.
Designations complement your existing IAM controls rather than replace them, and they provide one consistent authorization layer across every user type that SageMaker Unified Studio supports. This matters because SageMaker Unified Studio supports IAM roles, IAM users, SSO users, and SSO groups. You can’t attach IAM policies directly to SSO users or groups within SageMaker Unified Studio. Designations apply uniformly to all of these principals, so every user type is governed by the same permission model within a project.
Authorization happens in two layers. First, IAM evaluates whether a principal can invoke an API at the AWS API boundary. If IAM allows the call, the designation then evaluates whether the assigned permission set grants the specific action within the project. You don’t need to modify your existing IAM policies to adopt designations, but we still recommend that you continue to scope IAM roles to least privilege.
For example, the AmazonSageMakerDomainExecution role might hold the IAM permission to perform an API action such as datazone:CreateListingChangeSet, the permission to publish a data asset. The next layer is the designation: the action succeeds only if the project member’s designation includes the Manage Asset Publishing permission to publish assets in that project. Both layers must allow the action, and an IAM Deny blocks the call regardless of what the designation permits.
The following diagram shows how a project member’s request to publish a data set passes through both authorization layers.
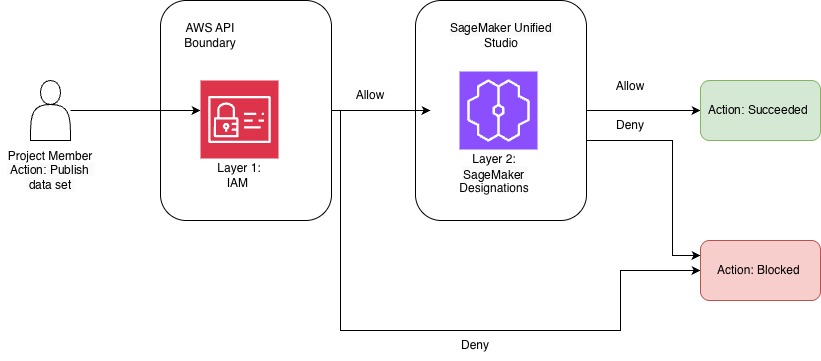
Figure 1: How a request to publish a data set passes through the IAM and designation authorization layers
The request first reaches the AWS API boundary, where IAM (layer 1) evaluates whether the principal can call the API. If IAM denies the call, the action is blocked. If IAM allows it, SageMaker Unified Studio (layer 2) evaluates the member’s designation. The action succeeds only when the designation also allows it. Otherwise, the action is blocked.
Managed designations
Every domain includes two AWS managed designations at the project level so you can start immediately:
- Owner – Full control over all project resources, including project member management.
- Contributor – Full access except for project member management and project deletion. Because Contributor is broad, we recommend custom designations for personas that don’t need full access.
You can view the permissions for these managed designations, but you can’t edit or delete them. To create your own permission sets, you build custom designations for the personas your organization needs.
Create a designation on the console
Designations are created and managed from the domain management portal. Only users whose profile is a domain administrator can access it. The domain management portal is separate from the Amazon SageMaker Unified Studio portal where members do their day-to-day work. In this example, we create an ML Engineer designation for members who build workloads through notebooks.
- Sign in to the SageMaker Unified Studio domain management portal.
- In the navigation pane, choose Designations. The Managed tab shows the AWS managed Owner and Contributor designations.
- Choose Create designation.
- For Name, enter
ML Engineer, and add a Description. - In the visual permission selector, expand the Notebook category and select only the permissions this persona requires, for example, Read-only actions for reviewers, or All Actions only for members who author notebooks.
- Choose Create.
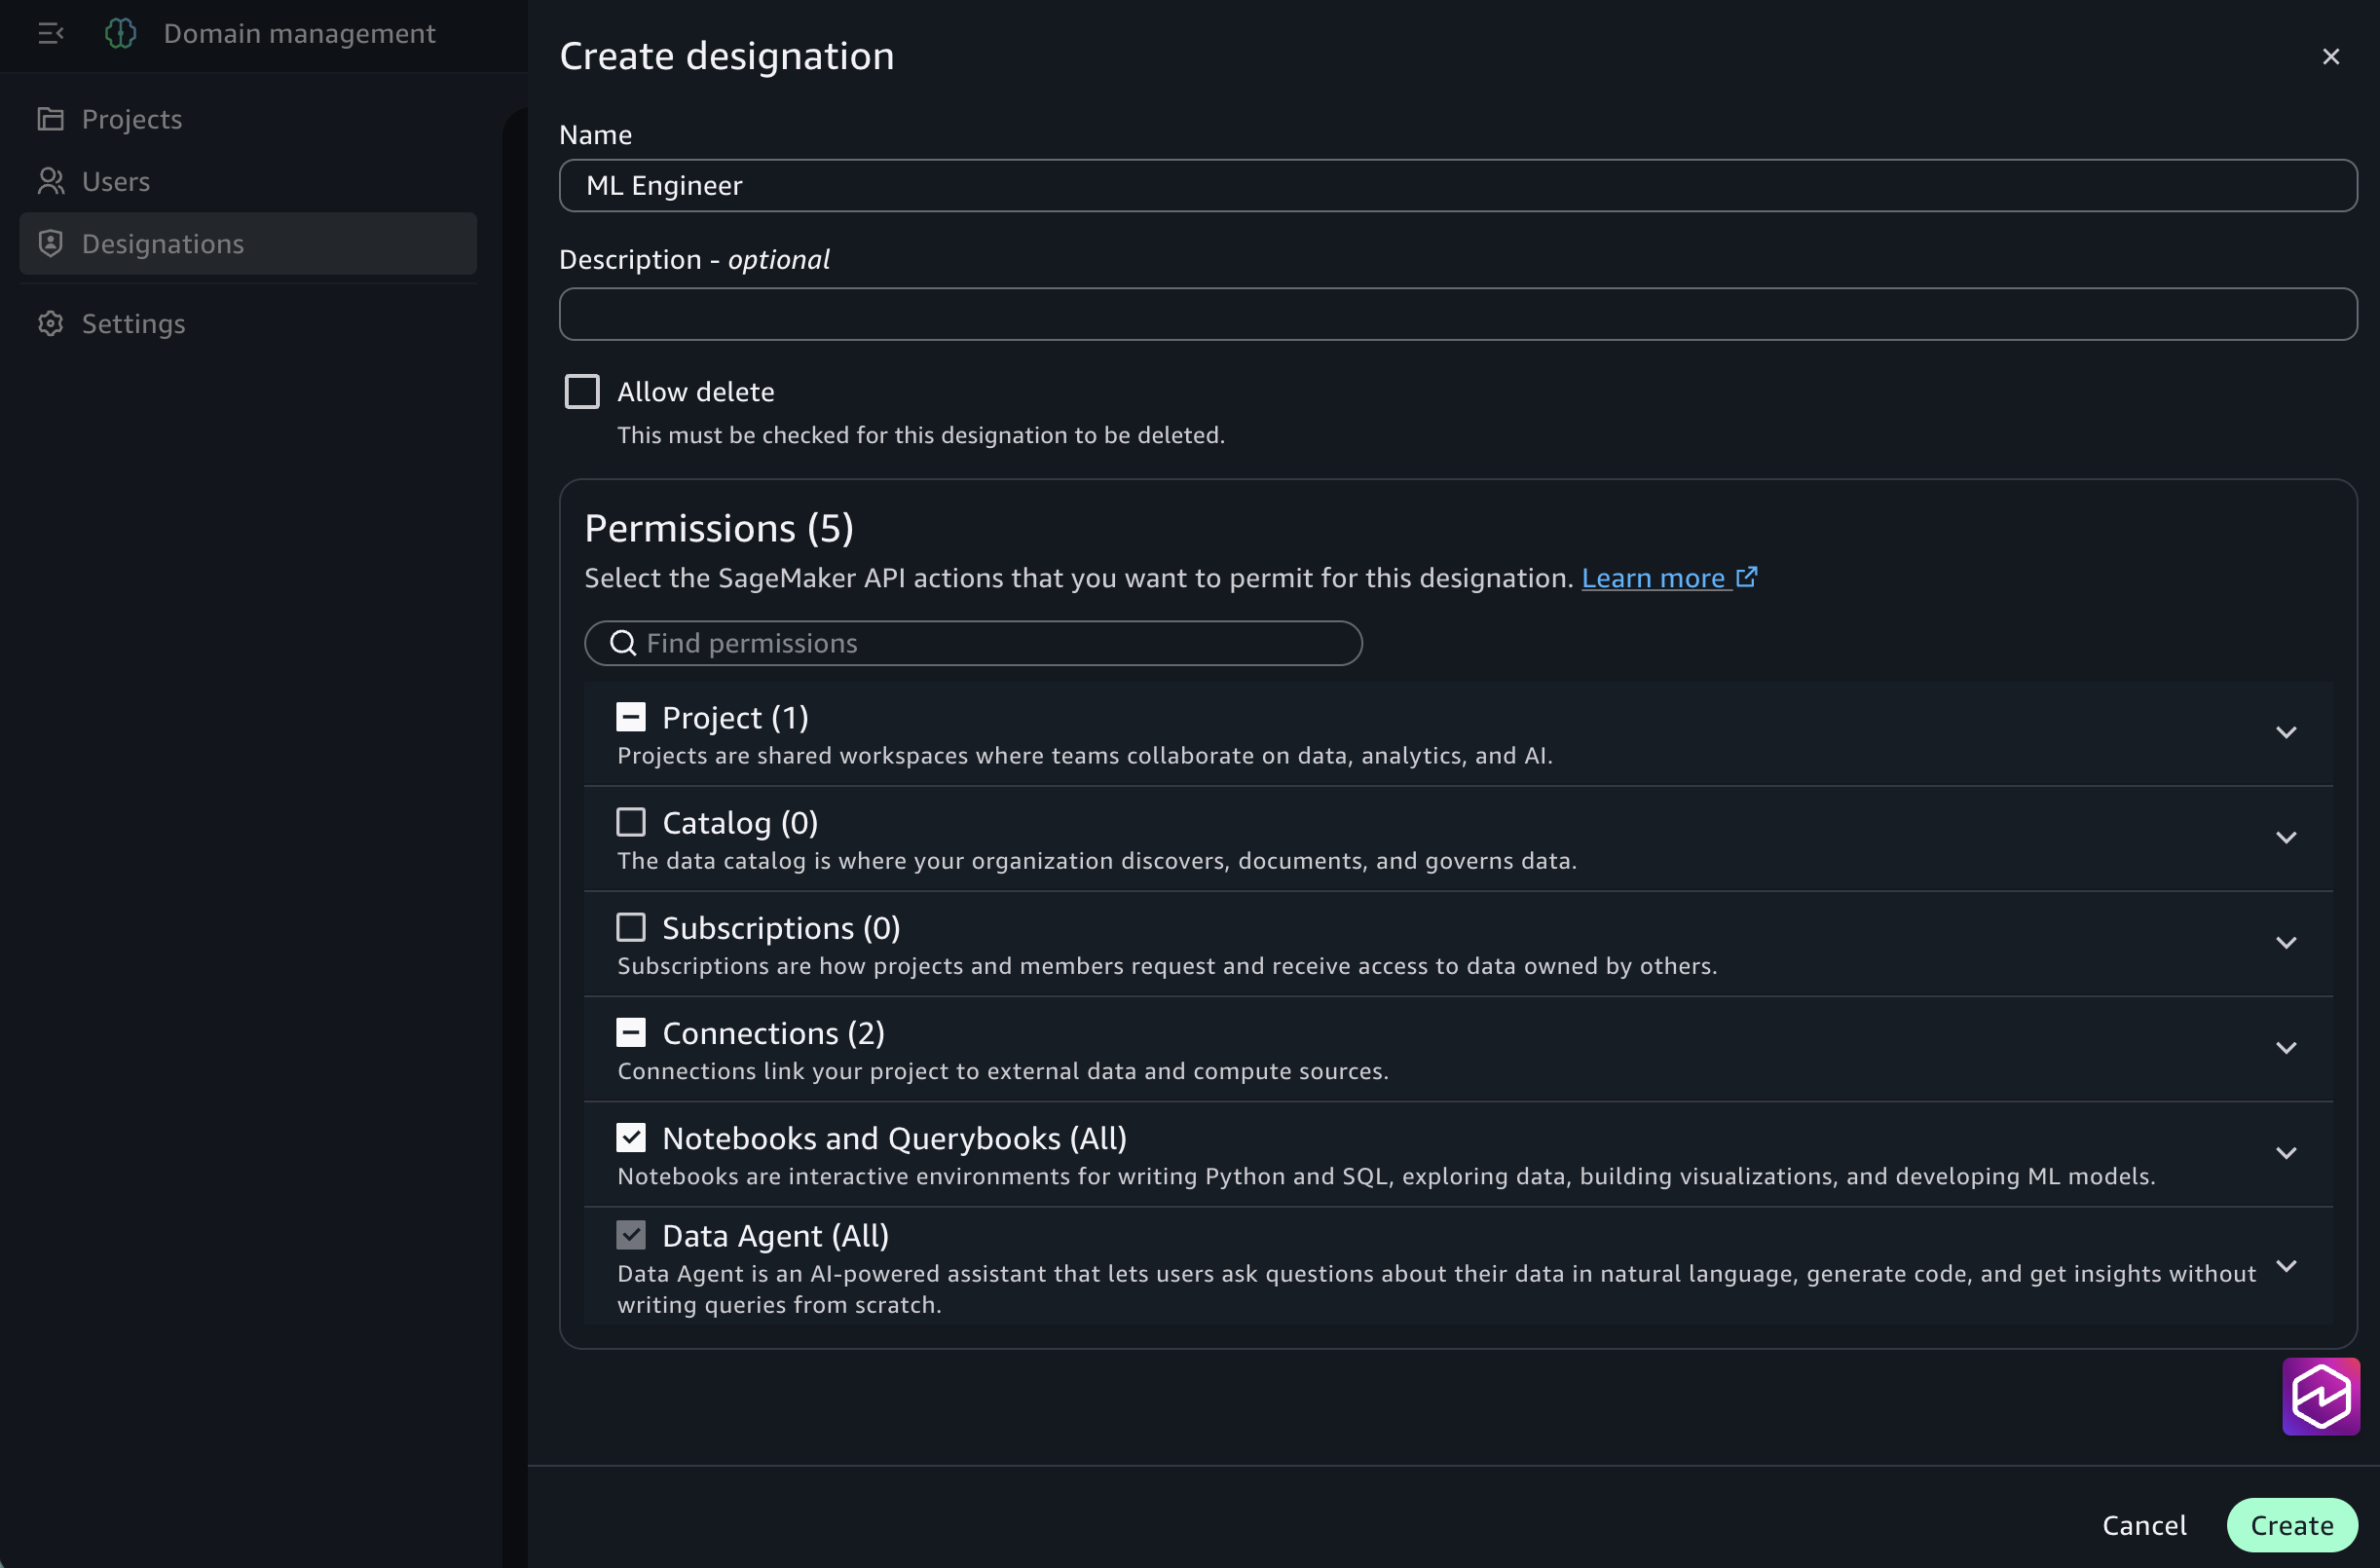
Figure 2: Creating a designation in the Amazon SageMaker Unified Studio domain management portal, using the visual permission selector to choose the actions to include
The ML Engineer designation is now available to every project in the domain. You can also create a designation by duplicating an existing one, which pre-selects a set of permissions for you to customize. Review the pre-selected permissions and remove any that the new persona doesn’t need.
Assign a designation to a project member
After creation, a designation is available to every project in the domain. You can assign it from two places, depending on your domain type.
From the SageMaker Unified Studio portal (Identity Center-based domains), assign the designation from a project where you are an owner, or if your designation has the Manage Membership permission. Grant Manage Membership only to trusted project members. A member who has the Manage Membership permission can assign designations with more permissions than their own.
- Navigate to the project in the SageMaker Unified Studio portal.
- Choose the Members tab.
- To update an existing member, choose a designation from the Designation column for that user. To add a new member, choose Add member and select the member.
- For Designation, choose ML Engineer.
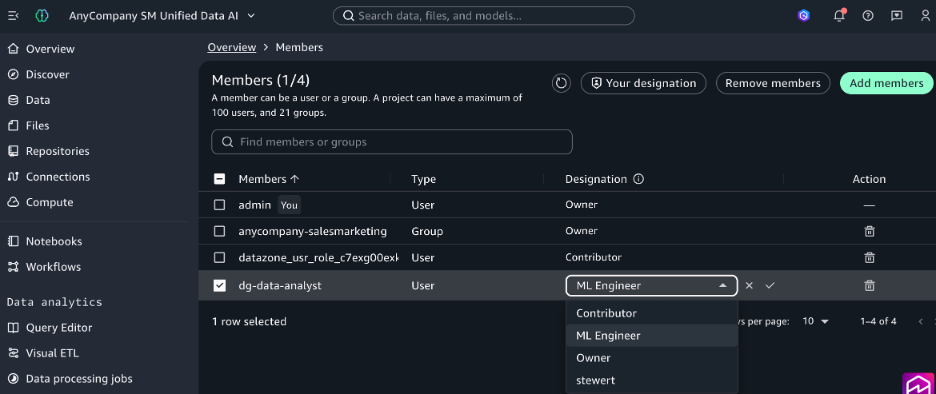
Figure 3: Assigning a designation to a project member from the Amazon SageMaker Unified Studio portal (Identity Center-based domains) using the Role list on the Members tab
From the domain management portal (both IAM and Identity Center-based domains):
- Sign in to the domain management portal and choose Projects in the navigation pane.
- Select the project, then choose the Members tab.
- To update an existing member, choose a designation from the Project designation column. To add a new member, choose Add members and select the type and member.
- For Designation, choose the designation to assign, then choose Save.
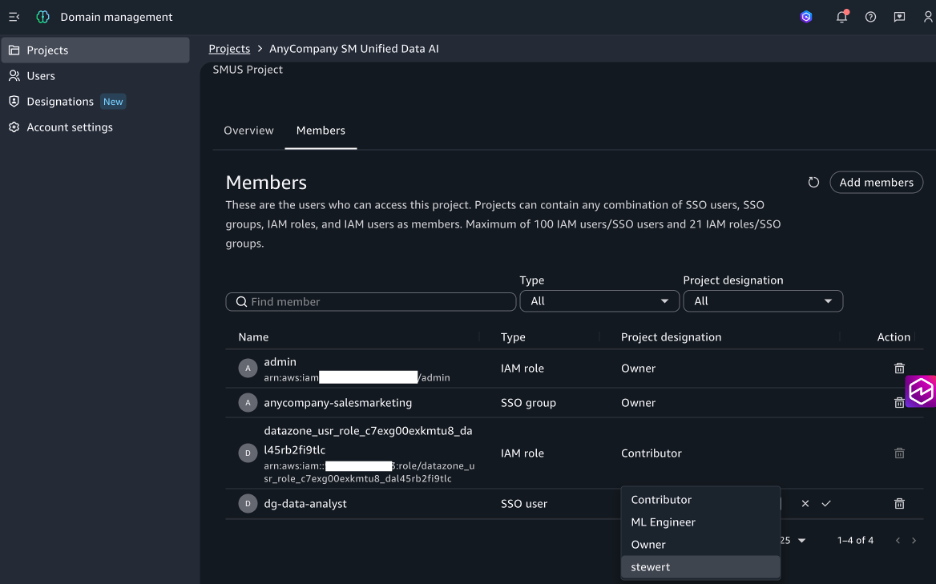
Figure 4: Assigning a designation from the domain management portal (both IAM and Identity Center-based domains) using the Project designation column on the Members tab
When the assigned user logs in to the project, they are permitted to create notebooks. Every project member is assigned a designation. Members without a valid designation have no permissions in the project.
Automate the full lifecycle with the AWS CLI and infrastructure as code (IaC)
You can manage the entire lifecycle, from creating a designation to assigning it, programmatically. This is useful for codifying governance and rolling it out at scale.
Prerequisites:
The IAM principal that runs these commands needs permissions (scoped to the domain) such as datazone:CreateDesignation, datazone:UpdateDesignation, and datazone:DeleteDesignation to manage designations. They need datazone:CreateProjectMembership to assign the designation to project members. Grant only the actions you need.
Create a designation with the AWS CLI:
Assign the designation when you add a member to a project:
Because designations are supported as resources in AWS CloudFormation, you can define them in your templates, version them in source control, and deploy them across domains through your existing infrastructure-as-code pipelines. You can also manage assignments with the CreateProjectMembership and UpdateProjectMembership API operations, so the full workflow can be automated without using the console.
Update designations as your needs evolve
When you update a designation’s permissions, the change takes effect immediately for all members assigned that designation across all projects, with no reassignment required. This means you can start with the minimum permissions each persona needs, and add permissions as requirements or new capabilities emerge. Because updates apply immediately across all projects, review designation changes through your change-management process and use AWS CloudTrail to audit them.
Delete a designation
Designations include an Allow delete property that is turned off by default, so a designation can’t be deleted until you explicitly allow it. When you create or edit a designation, set Allow delete to make the designation eligible for deletion. Once allowed, you can delete the designation even if project members are still assigned to it.
When you delete a designation that is still in use, those members remain in the project, but their assigned designation becomes invalid. They have no permissions in the project until the project owner reassigns them a valid designation. Plan deletions accordingly so members are not left without access.
You can also set this property programmatically. The CreateDesignation API and AWS CLI accept a deletion protection parameter, so you can codify the setting in your infrastructure as code templates.
To create the designation without delete protection, use the --no-deletion-protection flag.
Conclusion
Designations give administrators control over who can do what within each Amazon SageMaker Unified Studio project. Define named permission sets once and assign them per project to help enforce separation of duties across data engineers, stewards, analysts, ML engineers, and automated pipelines. You don’t need to duplicate projects or build a permission system outside SageMaker Unified Studio. Designations require no additional infrastructure or cost, integrate with AWS CloudFormation, and layer cleanly on top of your existing IAM controls.
To get started, open the domain management portal for your Amazon SageMaker Unified Studio domain, choose Designations, and create your first permission set. To learn more, see the Amazon SageMaker Unified Studio documentation.