Tag Archives: cryptomining

Detecting and preventing crypto mining in your AWS environment

Post Syndicated from Jason Palmer original https://aws.amazon.com/blogs/security/detecting-and-preventing-crypto-mining-in-your-aws-environment/

This article guides you on how to use Amazon GuardDuty to identify and mitigate cryptocurrency mining threats in your Amazon Web Services (AWS) environment. You’ll learn about the specialized detection capabilities of GuardDuty and best practices to build a multi-layered defense strategy that protects your infrastructure costs and security posture.

Understanding the crypto mining challenge

Crypto mining in AWS environments represents a notable security challenge that extends beyond basic resource consumption.

When threat actors gain unauthorized access to cloud resources for mining operations, organizations face multiple consequences:

  • Cost increases that can range from hundreds to thousands of dollars.
  • Performance degradation that can affect legitimate workloads.
  • Potential additional security incidents that can lead to data exposure or ransomware deployment.

The complexity of crypto mining incidents continues to evolve, with unauthorized users employing advanced techniques to evade detection while maximizing resource use. Organizations often discover these intrusions only after they experience the financial effects or when resource exhaustion affects business operations.

When crypto mining indicates broader system vulnerabilities, additional concerns arise. Unauthorized users who gain access for mining purposes can install backdoors, expose sensitive data through compromised credentials, or create pathways for lateral movement within your AWS infrastructure.

Identifying signs of crypto mining activity

Organizations must remain vigilant for several key indicators of crypto mining activities. These indicators include connections to unknown IP addresses or the use of known mining pool ports, such as 3333. Sustained high CPU or GPU usage that doesn’t align with normal business operations can also signal mining activity. Unexpected network traffic patterns, particularly spikes to unfamiliar IP addresses, also warrant investigation.

Security teams must monitor for unfamiliar processes or applications that run without authorization on their resources.

How GuardDuty detects crypto mining

GuardDuty employs advanced detection methods specifically designed to identify crypto mining activities across your AWS environment. The service uses machine learning algorithms to analyze multiple data sources. These data sources are trained on global threat data gathered by AWS, anomaly detection that establishes behavioral baselines, and integrated threat intelligence from AWS Security and partners.

GuardDuty’s crypto mining detection capabilities include several specialized finding types:

GuardDuty monitors Amazon Virtual Private Cloud (Amazon VPC) Flow Logs for suspicious network patterns and analyzes DNS queries for mining-related domains. GuardDuty also scrutinizes AWS CloudTrail events for suspicious API calls and collects workload telemetry when you turn on Runtime Monitoring. This comprehensive approach allows for detection across Amazon EC2 instances, Amazon Elastic Container Service (Amazon ECS) clusters, Kubernetes environments, and standalone containers.

When you turn on the Runtime Monitoring feature, GuardDuty deploys lightweight agents that provide deeper visibility into runtime processes and system behavior, and enables findings such as CryptoCurrency:Runtime/BitcoinTool.B and Impact:Runtime/CryptoMinerExecuted. These findings detect crypto mining software that operates within your workloads. For containerized environments, Amazon Elastic Kubernetes Service (Amazon EKS) findings can indicate when unauthorized access is potentially used for crypto mining operations.

Building multilayered protection against crypto mining

Organizations typically find that crypto mining protection benefits from multiple security layers, with the detection capabilities provided by GuardDuty forming one component of a broader security strategy. Consider turning on GuardDuty across all AWS accounts and AWS Regions through AWS Organizations. Activated Runtime Monitoring and Amazon EKS protection features provide comprehensive coverage.

The following actions can enhance GuardDuty capabilities:

  • Configure Amazon CloudWatch to monitor resource use metrics and set alarms for unusual CPU, network, or GPU usage spikes that might indicate mining activity. Implement AWS Config rules to verify that security configurations are compliant. These checks make sure that security groups don’t allow broad internet access, and that IMDSv2 is enforced.
  • Deploy AWS Network Firewall to enable granular outbound filtering and allow necessary internet connectivity while blocking access to crypto mining infrastructure.
  • Deploy AWS Systems Manager to maintain visibility into instance configurations. Inventory, a capability of Systems Manager, tracks installed applications to detect mining software. Additionally, Run Command and State Manager—capabilities of Systems Manager—enforce security policies across your fleet.
  • Create automated remediation workflows that use Amazon EventBridge and Lambda to respond immediately when GuardDuty detects crypto mining activities.

Best practices for comprehensive protection

Access management and authentication

  • To strengthen your preventive measures, implement least privilege access with AWS Identity and Access Management (IAM). For software use cases, use IAM roles inside of AWS and IAM Roles Anywhere outside of AWS instead of long-lived access keys. For human identities, centralize user management through AWS IAM Identity Center with multi-factor authentication (MFA) features, in addition to attribute-based access control for fine-grained permissions. If you don’t use Identity Center, then turn on MFA for all IAM users, including those with administrative privileges, and require MFA for sensitive operations.
  • If you can’t eliminate the use of long-lived access keys, then implement regular access key rotation policies and apply least privilege access to all IAM policies. Regularly audit IAM permissions to identify and remove excessive privileges.

System maintenance and configuration

  • Use Patch Manager, a capability of Systems Manager, to implement automated patching and maintain current Amazon Machine Images (AMIs) for all deployed EC2 instances. Establish a regular patch cadence for all systems and test patches in non-production environments before you deploy a patch.
  • Implement strict ingress rules in security groups and allow only necessary traffic. Use egress filtering to prevent unauthorized outbound connections to mining pools. Regularly audit security group configurations to make sure that the configurations meet security requirements.

Data protection

  • Use AWS Key Management Service (AWS KMS)S) to turn on encryption for all data at rest, and implement TLS for data in transit. AWS KMS uses envelope encryption by default, and protects your data keys with master keys to provide enhanced security and performance. It’s a best practice to regularly rotate encryption keys.

Benefits of comprehensive crypto mining protection

Organizations that implement these comprehensive security measures can experience the following improvements in their security posture and operational efficiency:

  • Reduced detection time: Detection times for crypto mining activities decrease from days or weeks to minutes so that teams can rapidly contain issues before significant damage occurs.
  • Automated responses: Automated response workflows reduce manual intervention requirements so that security teams can focus on strategic initiatives.
  • Cost control: These measures identify and terminate unauthorized resource consumption and prevent unexpected billing increases.
  • Performance stability: Crypto mining processes no longer monopolize CPU, memory, and network resources so that your organization can maintain application performance.
  • Enhanced visibility: The monitoring approach helps identify crypto mining and other security threats that might go unnoticed.
  • Team confidence: Security teams gain confidence through continuous monitoring and automated alerts. Teams can be secure in knowing that crypto mining attempts are promptly detected and addressed.

The implementation of preventive controls reduces the potential for initial incidents. Regular patching and configuration management further strengthen your overall security posture.

Crypto mining approval on AWS

AWS requires written approval for crypto mining activities on AWS under AWS Service Terms (Section 1.25). This requirement helps protect both your resources and the broader AWS infrastructure.

Requesting approval

AWS Trust & Safety reviews requests to help prevent mining activities from negatively affecting service performance or security. When submitting your request, include the following information:

  • Describe your mining purpose and business case.
  • Outline your infrastructure planning and cost management approach.
  • Detail your security measures to prevent unauthorized access.
  • Provide emergency contacts for rapid communication, if issues arise.
  • Specify the number of instances and type of crypto mining.

What to expect after approval

Approved mining operations must follow specific guidelines to maintain good standing. AWS monitors approved mining activities to verify that the activities don’t generate abuse reports, effect service performance, or deviate from prescribed architecture and security practices.

Important considerations

Review the following information:

  • You can’t use AWS Credits and Free Tier resources for crypto mining activities.
  • It’s essential to continuously monitor your mining resources.
  • Based on changing infrastructure conditions, AWS can adjust approvals.

This approval process distinguishes legitimate mining operations from unauthorized activities that might indicate security compromises.

Conclusion

To protect AWS environments against crypto mining, AWS Trust & Safety recommends taking a comprehensive approach that combines advanced threat detection with proactive security measures. GuardDuty provides foundational detection capabilities that help to identify crypto mining activities, while complementary AWS services create a robust security ecosystem that protects your infrastructure and data.

Security is a shared responsibility. While AWS provides powerful tools and services designed to be highly secure, your organization’s implementation of security practices and controls determines your overall protection level. Regular review and updates of your security measures, as well as team training and awareness, help maintain an effective defense against crypto mining and other security threats in your AWS environment.

If you have feedback about this post, submit comments in the Comments section below.
Jason Palmer

Jason is a Senior Technical Account Manager (TAM) at AWS Enterprise Support, based in Seattle, Washington. With over 6 years at AWS, Jason combines deep technical expertise with a genuine passion for people — helping enterprise customers transform complex challenges into scalable cloud solutions.

Nadia Mahmood

Nadia is a Trust & Safety Customer Advisor at AWS, based in Virginia. Nadia works with enterprise customers on abuse reporting and compliance, handling escalated takedown requests and strategic partnerships to reduce abuse across AWS.

Contributors

Special thanks to James Ferguson, a Principal Solutions Architect and Jeffrey Bickford, a Security Engineering Manager, who made significant contributions to this post.

Cryptomining campaign targeting Amazon EC2 and Amazon ECS

Post Syndicated from Kyle Koeller original https://aws.amazon.com/blogs/security/cryptomining-campaign-targeting-amazon-ec2-and-amazon-ecs/

Amazon GuardDuty and our automated security monitoring systems identified an ongoing cryptocurrency (crypto) mining campaign beginning on November 2, 2025. The operation uses compromised AWS Identity and Access Management (IAM) credentials to target Amazon Elastic Container Service (Amazon ECS) and Amazon Elastic Compute Cloud (Amazon EC2). GuardDuty Extended Threat Detection was able to correlate signals across these data sources to raise a critical severity attack sequence finding. Using the massive, advanced threat intelligence capability and existing detection mechanisms of Amazon Web Services (AWS), GuardDuty proactively identified this ongoing campaign and quickly alerted customers to the threat. AWS is sharing relevant findings and mitigation guidance to help customers take appropriate action on this ongoing campaign.

It’s important to note that these actions don’t take advantage of a vulnerability within an AWS service but rather require valid credentials that an unauthorized user uses in an unintended way. Although these actions occur in the customer domain of the shared responsibility model, AWS recommends steps that customers can use to detect, prevent, or reduce the impact of such activity.

Understanding the crypto mining campaign

The recently detected crypto mining campaign employed a novel persistence technique designed to disrupt incident response and extend mining operations. The ongoing campaign was originally identified when GuardDuty security engineers discovered similar attack techniques being used across multiple AWS customer accounts, indicating a coordinated campaign targeting customers using compromised IAM credentials.

Operating from an external hosting provider, the threat actor quickly enumerated Amazon EC2 service quotas and IAM permissions before deploying crypto mining resources across Amazon EC2 and Amazon ECS. Within 10 minutes of the threat actor gaining initial access, crypto miners were operational.

A key technique observed in this attack was the use of ModifyInstanceAttribute with disable API termination set to true, forcing victims to re-enable API termination before deleting the impacted resources. Disabling instance termination protection adds an additional consideration for incident responders and can disrupt automated remediation controls. The threat actor’s scripted use of multiple compute services, in combination with emerging persistence techniques, represents an advancement in crypto mining persistence methodologies that security teams should be aware of.

The multiple detection capabilities of GuardDuty successfully identified the malicious activity through EC2 domain/IP threat intelligence, anomaly detection, and Extended Threat Detection EC2 attack sequences. GuardDuty Extended Threat Detection was able to correlate signals as an AttackSequence:EC2/CompromisedInstanceGroup finding.

Indicators of compromise (IoCs)

Security teams should monitor for the following indicators to identify this crypto mining campaign. Threat actors frequently modify their tactics and techniques, so these indicators might evolve over time:

  • Malicious container image – The Docker Hub image yenik65958/secret, created on October 29, 2025, with over 100,000 pulls, was used to deploy crypto miners to containerized environments. This malicious image contained a SBRMiner-MULTI binary for crypto mining. This specific image has been taken down from Docker Hub, but threat actors might deploy similar images under different names.
  • Automation and toolingAWS SDK for Python (Boto3) user agent patterns indicating Python-based automation scripts were used across the entire attack chain.
  • Crypto mining domains: asia[.]rplant[.]xyz, eu[.]rplant[.]xyz, and na[.]rplant[.]xyz.
  • Infrastructure naming patterns – Auto scaling groups followed specific naming conventions: SPOT-us-east-1-G*-* for spot instances and OD-us-east-1-G*-* for on-demand instances, where G indicates the group number.

Attack chain analysis

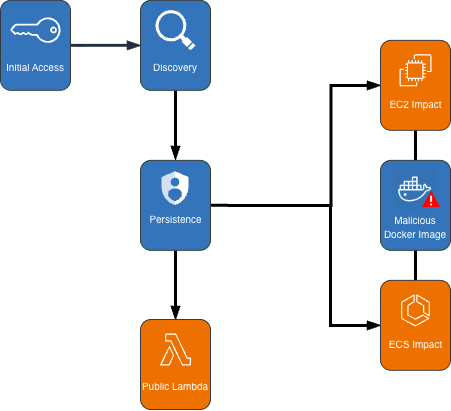
The crypto mining campaign followed a systematic attack progression across multiple phases. Sensitive fields in this post were given fictitious values to protect personally identifiable information (PII).

Cryptocurrency Mining Campaign Diagram

Figure 1: Cryptocurrency mining campaign diagram

Initial access, discovery, and attack preparation

The attack began with compromised IAM user credentials possessing admin-like privileges from an anomalous network and location, triggering GuardDuty anomaly detection findings. During the discovery phase, the attacker systematically probed customer AWS environments to understand what resources they could deploy. They checked Amazon EC2 service quotas (GetServiceQuota) to determine how many instances they could launch, then tested their permissions by calling the RunInstances API multiple times with the DryRun flag enabled.

The DryRun flag was a deliberate reconnaissance tactic that allowed the actor to validate their IAM permissions without actually launching instances, avoiding costs and reducing their detection footprint. This technique demonstrates the threat actor was validating their ability to deploy crypto mining infrastructure before acting. Organizations that don’t typically use DryRun flags in their environments should consider monitoring for this API pattern as an early warning indicator of compromise. AWS CloudTrail logs can be used with Amazon CloudWatch alarms, Amazon EventBridge, or your third-party tooling to alert on these suspicious API patterns.

The threat actor called two APIs to create IAM roles as part of their attack infrastructure: CreateServiceLinkedRole to create a role for auto scaling groups and CreateRole to create a role for AWS Lambda. They then attached the AWSLambdaBasicExecutionRole policy to the Lambda role. These two roles were integral to the impact and persistence stages of the attack.

Amazon ECS impact

The threat actor first created dozens of ECS clusters across the environment, sometimes exceeding 50 ECS clusters in a single attack. They then called RegisterTaskDefinition with a malicious Docker Hub image yenik65958/secret:user. With the same string used for the cluster creation, the actor then created a service, using the task definition to initiate crypto mining on ECS AWS Fargate nodes. The following is an example of API request parameters for RegisterTaskDefinition with a maximum CPU allocation of 16,384 units.

{   
    "dryrun": false,   
    "requiresCompatibilities": ["FARGATE"],   
    "cpu": 16384,   
    "containerDefinitions": [     
        {       
            "name": "a1b2c3d4e5",       
            "image": "yenik65958/secret:user",       
            "cpu": 0,       
            "command": []     
        }   
    ],   
    "networkMode": "awsvpc",   
    "family": "a1b2c3d4e5",   
    "memory": 32768 
}

Using this task definition, the threat actor called CreateService to launch ECS Fargate tasks with a desired count of 10.

{   
    "dryrun": false,   
    "capacityProviderStrategy": [     
        {       
            "capacityProvider": "FARGATE",       
            "weight": 1,       
            "base": 0     
        },     
        {       
            "capacityProvider": "FARGATE_SPOT",       
            "weight": 1,       
            "base": 0     
        }   
    ],   
    "desiredCount": 10 
}

Figure 2: Contents of the cryptocurrency mining script within the malicious image

Figure 2: Contents of the cryptocurrency mining script within the malicious image

The malicious image (yenik65958/secret:user) was configured to execute run.sh after it has been deployed. run.sh runs randomvirel mining algorithm with the mining pools: asia|eu|na[.]rplant[.]xyz:17155. The flag nproc --all indicates that the script should use all processor cores.

Amazon EC2 impact

The actor created two launch templates (CreateLaunchTemplate) and 14 auto scaling groups (CreateAutoScalingGroup) configured with aggressive scaling parameters, including a maximum size of 999 instances and desired capacity of 20. The following example of request parameters from CreateLaunchTemplate shows the UserData was supplied, instructing the instances to begin crypto mining.

{   
    "CreateLaunchTemplateRequest": {       
        "LaunchTemplateName": "T-us-east-1-a1b2",       
        "LaunchTemplateData": {           
            "UserData": "<sensitiveDataRemoved>",           
            "ImageId": "ami-1234567890abcdef0",           
            "InstanceType": "c6a.4xlarge"       
        },       
        "ClientToken": "a1b2c3d4-5678-90ab-cdef-EXAMPLE11111"   
    } 
}

The threat actor created auto scaling groups using both Spot and On-Demand Instances to make use of both Amazon EC2 service quotas and maximize resource consumption.

Spot Instance groups:

  • Targeted high performance GPU and machine learning (ML) instances (g4dn, g5, g5, p3, p4d, inf1)
  • Configured with 0% on-demand allocation and capacity-optimized strategy
  • Set to scale from 20 to 999 instances

On-Demand Instance groups:

  • Targeted compute, memory, and general-purpose instances (c5, c6i, r5, r5n, m5a, m5, m5n).
  • Configured with 100% on-demand allocation
  • Also set to scale from 20 to 999 instances

After exhausting auto scaling quotas, the actor directly launched additional EC2 instances using RunInstances to consume the remaining EC2 instance quota.

Persistence

An interesting technique observed in this campaign was the threat actor’s use of ModifyInstanceAttribute across all launched EC2 instances to disable API termination. Although instance termination protection prevents accidental termination of the instance, it adds an additional consideration for incident response capabilities and can disrupt automated remediation controls. The following example shows request parameters for the API ModifyInstanceAttribute.

{     
    "disableApiTermination": {         
        "value": true     
    },     
    "instanceId": "i-1234567890abcdef0" 
}

After all mining workloads were deployed, the actor created a Lambda function with a configuration that bypasses IAM authentication and creates a public Lambda endpoint. The threat actor then added a permission to the Lambda function that allows the principal to invoke the function. The following examples show CreateFunctionUrlConfig and AddPermission request parameters.

CreateFunctionUrlConfig:

{     
    "authType": "NONE",     
    "functionName": "generate-service-a1b2c3d4" 
}

AddPermission:

{     
    "functionName": "generate-service-a1b2c3d4",     
    "functionUrlAuthType": "NONE",    
    "principal": "*",     
    "statementId": "FunctionURLAllowPublicAccess",     
    "action": "lambda:InvokeFunctionUrl" 
}

The threat actor concluded the persistence stage by creating an IAM user user-x1x2x3x4 and attaching the IAM policy AmazonSESFullAccess (CreateUser, AttachUserPolicy). They also created an access key and login profile for that user (CreateAccessKey, CreateLoginProfile). Based on the SES role that was attached to the user, it appears the threat actor was attempting Amazon Simple Email Service (Amazon SES) phishing.

To prevent public Lambda URLs from being created, organizations can deploy service control policies (SCPs) that deny creation or updating of Lambda URLs with an AuthType of “NONE”.

{   
    "Version": "2012-10-17",   
    "Statement": [     
        {       
            "Effect": "Deny",       
            "Action": [         
                "lambda:CreateFunctionUrlConfig",         
                "lambda:UpdateFunctionUrlConfig"       
            ],       
            "Resource": "arn:aws:lambda:*:*:function/*",       
            "Condition": {         
                "StringEquals": {           
                    "lambda:FunctionUrlAuthType": "NONE"         
                }       
            }     
        }   
    ] 
}

Detection methods using GuardDuty

The multilayered detection approach of GuardDuty proved highly effective in identifying all stages of the attack chain using threat intelligence, anomaly detection, and the recently launched Extended Threat Detection capabilities for EC2 and ECS.

Next, we walk through the details of these features and how you can deploy them to detect attacks such as these. You can enable GuardDuty foundational protection plan to receive alerts on crypto mining campaigns like the one described in this post. To further enhance detection capabilities, we highly recommend enabling GuardDuty Runtime Monitoring, which will extend finding coverage to system-level events on Amazon EC2, Amazon ECS, and Amazon Elastic Kubernetes Service (Amazon EKS).

GuardDuty EC2 findings

Threat intelligence findings for Amazon EC2 are part of the GuardDuty foundational protection plan, which will alert you to suspicious network behaviors involving your instances. These behaviors can include brute force attempts, connections to malicious or crypto domains, and other suspicious behaviors. Using third-party threat intelligence and internal threat intelligence, including active threat defense and MadPot, GuardDuty provides detection over the indicators in this post through the following findings: CryptoCurrency:EC2/BitcoinTool.B and CryptoCurrency:EC2/BitcoinTool.B!DNS.

GuardDuty IAM findings

The IAMUser/AnomalousBehavior findings spanning multiple tactic categories (PrivilegeEscalation, Impact, Discovery) showcase the ML capability of GuardDuty to detect deviations from normal user behavior. In the incident described in this post, the compromised credentials were detected due to the threat actor using them from an anomalous network and location and calling APIs that were unusual for the accounts.

GuardDuty Runtime Monitoring

GuardDuty Runtime Monitoring is an important component for Extended Threat Detection attack sequence correlation. Runtime Monitoring provides host level signals, such as operating system visibility, and extends detection coverage by analyzing system-level logs indicating malicious process execution at the host and container level, including the execution of crypto mining programs on your workloads. The CryptoCurrency:Runtime/BitcoinTool.B!DNS and CryptoCurrency:Runtime/BitcoinTool.B findings detect network connections to crypto-related domains and IPs, while the Impact:Runtime/CryptoMinerExecuted finding detects when a process running is associated with a cryptocurrency mining activity.

GuardDuty Extended Threat Detection

Launched at re:Invent 2025, AttackSequence:EC2/CompromisedInstanceGroup finding represents one of the latest Extended Threat Detection capabilities in GuardDuty. This feature uses AI and ML algorithms to automatically correlate security signals across multiple data sources to detect sophisticated attack patterns of EC2 resource groups. Although AttackSequences for EC2 are included in the GuardDuty foundational protection plan, we strongly recommend enabling Runtime Monitoring. Runtime Monitoring provides key insights and signals from compute environments, enabling detection of suspicious host-level activities and improving correlation of attack sequences. For AttackSequence:ECS/CompromisedCluster attack sequences, Runtime Monitoring is required to correlate container-level activity.

Monitoring and remediation recommendations

To protect against similar crypto mining attacks, AWS customers should prioritize strong identity and access management controls. Implement temporary credentials instead of long-term access keys, enforce multi-factor authentication (MFA) for all users, and apply least privilege to IAM principals limiting access to only required permissions. You can use AWS CloudTrail to log events across AWS services and combine logs into a single account to make them available to your security teams to access and monitor. To learn more, refer to Receiving CloudTrail log files from multiple accounts in the CloudTrail documentation.

Confirm GuardDuty is enabled across all accounts and Regions with Runtime Monitoring enabled for comprehensive coverage. Integrate GuardDuty with AWS Security Hub and Amazon EventBridge or third-party tooling to enable automated response workflows and rapid remediation of high-severity findings. Implement container security controls, including image scanning policies and monitoring for unusual CPU allocation requests in ECS task definitions. Finally, establish specific incident response procedures for crypto mining attacks, including documented steps to handle instances with disabled API termination—a technique used by this attacker to complicate remediation efforts.

If you believe your AWS account has been impacted by a crypto mining campaign, refer to remediation steps in the GuardDuty documentation: Remediating potentially compromised AWS credentials, Remediating a potentially compromised EC2 instance, and Remediating a potentially compromised ECS cluster.

To stay up to date on the latest techniques, visit the Threat Technique Catalog for AWS.


If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, contact AWS Support.

Kyle Koeller
Kyle Koeller

Kyle is a security engineer in the GuardDuty team with a focus on threat detection. He is passionate about cloud threat detection and offensive security, and he holds the following certifications: CompTIA Security+, PenTest+, CompTIA Network Vulnerability Assessment Professional, and SecurityX. When not working, Kyle enjoys spending his time in the gym and exploring New York City.

AWS CIRT announces the release of five publicly available workshops

Post Syndicated from Steve de Vera original https://aws.amazon.com/blogs/security/aws-cirt-announces-the-release-of-five-publicly-available-workshops/

Greetings from the AWS Customer Incident Response Team (CIRT)! AWS CIRT is dedicated to supporting customers during active security events on the customer side of the AWS Shared Responsibility Model.

Over the past year, AWS CIRT has responded to hundreds of such security events, including the unauthorized use of AWS Identity and Access Management (IAM) credentials, ransomware and data deletion in an AWS account, and billing increases due to the creation of unauthorized resources to mine cryptocurrency.

We are excited to release five workshops that simulate these security events to help you learn the tools and procedures that AWS CIRT uses on a daily basis to detect, investigate, and respond to such security events. The workshops cover AWS services and tools, such as Amazon GuardDuty, Amazon CloudTrail, Amazon CloudWatch, Amazon Athena, and AWS WAF, as well as some open source tools written and published by AWS CIRT.

To access the workshops, you just need an AWS account, an internet connection, and the desire to learn more about incident response in the AWS Cloud! Choose the following links to access the workshops.

Unauthorized IAM Credential Use – Security Event Simulation and Detection

During this workshop, you will simulate the unauthorized use of IAM credentials by using a script invoked within AWS CloudShell. The script will perform reconnaissance and privilege escalation activities that have been commonly seen by AWS CIRT and that are typically performed during similar events of this nature. You will also learn some tools and processes that AWS CIRT uses, and how to use these tools to find evidence of unauthorized activity by using IAM credentials.

Ransomware on S3 – Security Event Simulation and Detection

During this workshop, you will use an AWS CloudFormation template to replicate an environment with multiple IAM users and five Amazon Simple Storage Service (Amazon S3) buckets. AWS CloudShell will then run a bash script that simulates data exfiltration and data deletion events that replicate a ransomware-based security event. You will also learn the tools and processes that AWS CIRT uses to respond to similar events, and how to use these tools to find evidence of unauthorized S3 bucket and object deletions.

Cryptominer Based Security Events – Simulation and Detection

During this workshop, you will simulate a cryptomining security event by using a CloudFormation template to initialize three Amazon Elastic Compute Cloud (Amazon EC2) instances. These EC2 instances will mimic cryptomining activity by performing DNS requests to known cryptomining domains. You will also learn the tools and processes that AWS CIRT uses to respond to similar events, and how to use these tools to find evidence of unauthorized creation of EC2 instances and communication with known cryptomining domains.

SSRF on IMDSv1 – Simulation and Detection

During this workshop, you will simulate the unauthorized use of a web application that is hosted on an EC2 instance configured to use Instance Metadata Service Version 1 (IMDSv1) and vulnerable to server side request forgery (SSRF). You will learn how web application vulnerabilities, such as SSRF, can be used to obtain credentials from an EC2 instance. You will also learn the tools and processes that AWS CIRT uses to respond to this type of access, and how to use these tools to find evidence of the unauthorized use of EC2 instance credentials through web application vulnerabilities such as SSRF.

AWS CIRT Toolkit For Automating Incident Response Preparedness

During this workshop, you will install and experiment with some common tools and utilities that AWS CIRT uses on a daily basis to detect security misconfigurations, respond to active events, and assist customers with protecting their infrastructure.

If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, contact AWS Support.

Want more AWS Security news? Follow us on Twitter.

Author

Steve de Vera

Steve is the Incident Response Watch Lead for the US Pacific region of the AWS CIRT. He is passionate about American-style BBQ and is a certified competition BBQ judge. He has a dog named Brisket.