All posts by Rapid7

7 Rapid Questions on our Belfast Placement Programme: Orla Magee and Paddy McDermott

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/10/18/7-rapid-questions-on-our-belfast-placement-programme-orla-magee-and-paddy-mcdermott/
7 Rapid Questions on our Belfast Placement Programme: Orla Magee and Paddy McDermott

Ever wonder what it’s like to be an intern at Rapid7 in Belfast?

Software Engineers Orla Magee and Paddy McDermott share what the interview process looked like for them, along with impactful projects and advice for others exploring Rapid7’s Placement Programme.

What was the interview process like for the Placement Programme?

Paddy: The interview process for Rapid7’s Placement Programme was well structured and welcoming. It consisted of two parts, a one-on-one chat focusing on cultural alignment, and a technical interview with programming questions and a puzzle to solve. The interviewers were approachable, which helped me feel at ease. I felt as though they struck a good balance, assessing my skills without overwhelming me with information and questions. It felt like a genuine attempt to get to know me as a person and assess my skills, rather than just ticking boxes.

Orla: From the start, the talent acquisition team was friendly and communicative, keeping me well-informed about each stage. The interviewers seemed genuinely interested in getting to know me as a person, highlighting that being yourself is crucial in this process. Overall, the interview experience reflected positively on Rapid7’s commitment to finding well-rounded individuals who can contribute both technically and culturally to their team, which made me feel at ease and excited for an opportunity to work at Rapid7.

What initially stood out to you about Rapid7?

Paddy: What stood out to me about Rapid7 was the genuine connection I felt with the people I met during the interview process. The interviewers were engaging and approachable, which gave me a strong sense of the company’s collaborative culture. Another thing that caught my attention was Rapid7’s commitment to growing new talent. This became clear when I attended an event specifically for intern applicants, where I got to experience the company’s welcoming atmosphere firsthand. A mix of friendly people, a learning-focused environment and the opportunity for significant professional growth really made Rapid7 stand out as an ideal place to begin my career.

What was the learning curve like coming into Rapid7 as a student, and what resources or tools did you have to navigate that?

Orla: Transitioning from university to working at Rapid7 as a student came with a significant learning curve. In university, I was used to working independently on projects. At Rapid7, I had to adapt to collaborating as part of a team. This shift required developing my communication skills and learning to work effectively with others. Additionally, the codebase was much bigger and more complex than the smaller-scale projects I had worked on in university. To help navigate these challenges, I was paired with a mentor at the start of my internship, who was instrumental in developing my technical abilities and helping me adjust to working in a professional environment. Alongside my mentor, my team members were always willing to offer assistance and guidance, creating a supportive atmosphere that facilitated my learning and growth. This combination of mentorship and team support was crucial in helping me overcome the learning curve and successfully adapt to a new work environment.

Can you share a memorable project or experience?

Paddy: One of my most memorable achievements during my placement was developing a full-stack status page. This project was particularly significant as it served a real, practical purpose within the company. The status page I created was designed to alert on outages and display the health of various components of our team’s pipeline. This tool was used beyond our team, and was shared internally across different parts of the company. This project allowed me to greatly expand my full-stack development skills in a meaningful way. It was rewarding to see something I built from the ground up being actively used to improve monitoring and communication about our pipeline’s status.

What advice would you give someone looking to land a Placement with Rapid7?

Orla: Take advantage of intern nights, held at the office, as these events offer a unique glimpse into Rapid7’s culture and team dynamics. These events are great opportunities to network and build connections with current staff members, potentially giving you an insider’s perspective on the company.

Paddy: My main advice would be to be yourself throughout the whole process as this will really   help you connect with the interviewers and showcase your true potential. Also, make sure to demonstrate a strong willingness to learn, as Rapid7 values candidates who are eager to grow and take on new challenges.

What were some of your biggest fears coming in, And how did that compare to reality?

Orla: When I started my internship at Rapid7, my main concern was that my technical skills might not measure up to those of my peers. I worried about potentially struggling to contribute meaningfully to the team, but my real experience showed that these worries were unnecessary. From day one, I was met with a welcoming and supportive environment. My colleagues were not only understanding of my position as an intern but were also genuinely enthusiastic about helping me develop my skills. They took the time to walk me through their current projects, providing valuable context and insights that helped me quickly get up to speed. My initial uncertainty was replaced with excitement for the opportunity to learn and contribute, and the reality of the internship far exceeded my expectations.

How has your placement experience prepared you for a successful career?

Paddy: Overall, the placement has given me a mix of technical growth, hands-on experience and professional development creating a strong foundation for my future in tech. I’ve learned many new programming languages with guidance from experienced colleagues. Working in a live production environment has equipped me with real-world skills and experiences. Presenting demos has boosted my confidence in public speaking and taught me how to communicate technical concepts effectively. I’ve built connections and friendships with coworkers which has made the work environment enjoyable and allowed me to start to form a professional network that will be valuable in my career.

Interested in learning more about the Placement Programme, or additional emerging talent programmes at Rapid7? Click here to explore our offerings and view open jobs.
Root Access for Data Control: A DEF CON IoT Village Story

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/10/16/root-access-for-data-control-a-def-con-iot-village-story/

Root Access for Data Control: A DEF CON IoT Village Story

Every year, Rapid7 is a presenter at DEF CON’s IoT Village, sharing in-depth insight and expertise into the hacking of all things Internet of Things. This year, our perennial IoT hacking presenter, Principal Security Researcher, IoT, Deral Heiland, along with Rapid7 pentest team members, showed attendees many methods of extracting firmware from IoT devices and manipulating the systems in the name of control and operations.

Extracting firmware without the use of destructive means can be difficult and in some cases impossible. However, Deral went deep with IoT Village attendees, presenting a live hands-on exercise each attendee in the room could interact with. It was an enlightening and productive presentation. But we are aware not everyone could make it to DEF CON 32 this year.

Which is why we’ve transformed the presentation into a handy whitepaper. Deral has gone step-by-step through the exercise, and even improved upon it in some cases (so even if you were in the room, there’s likely even more for you to get from it). While DEF CON 32 may be firmly in the rear-view mirror, the hacking carries on. And if you missed DEF CON, or Deral’s presentation, you have another chance to learn and take part in the exercise.

To check out the whitepaper, please click here. And if you’d like to learn more about Deral’s previous IoT Village presentations (he’s done a lot of them), many live right here on the blog.

Test Driving a New Benefit Programme in Belfast

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/10/16/test-driving-a-new-benefit-programme-in-belfast/

Test Driving a New Benefit Programme in Belfast

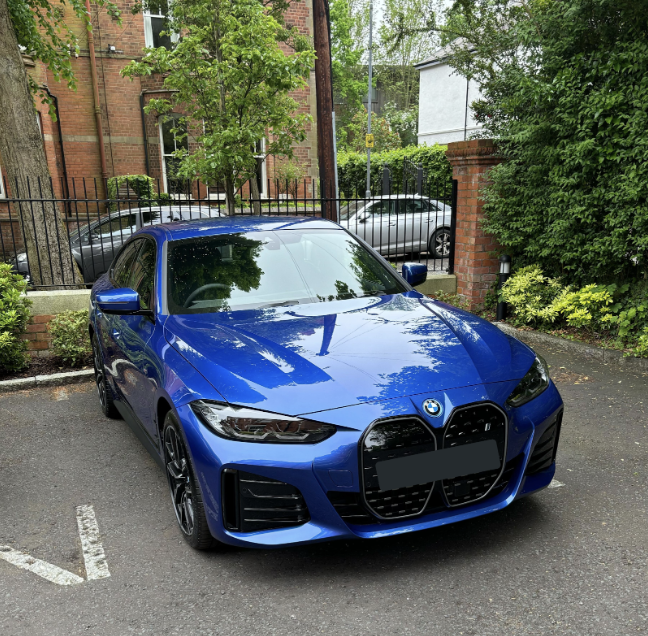
When most people think about benefits packages at work, what typically comes to mind are things like healthcare programmes, financial stipends, or wellbeing incentives. For Stephen, one benefit he uses on a daily basis comes on four wheels.

Rapid7’s electric vehicle scheme was rolled out in late 2023 for Belfast employees. The programme enables employees to lease an electric car via their employer and pay for it on a salary sacrifice basis, offering substantial tax and national insurance savings.

“I kept reading about the program and thinking – is it really this simple? What’s the catch?” said Stephen Gallagher, a Lead Product Manager who received his new electric BMW this past May. “The more I learned about the process and understood what that pre-tax payment would be vs. paying for a vehicle on my own, it was really a no brainer.”

The unique offering also contributes to the company’s sustainability goals by making electric vehicles more accessible, thanks to the pre-tax salary sacrifice. “I’ve worked for some other big tech companies in Belfast, but I’ve never seen this as a company offering. It definitely gives me a great sense of pride to work for Rapid7, and I feel motivated to do well for a company that takes care of employees in such a unique way.”

Test Driving a New Benefit Programme in Belfast

“The program provides employees with make and model options based on different salary levels to ensure the monthly payment is reasonable. Once an employee enrolls and selects a vehicle, our vendor sources it and coordinates delivery. Employees don’t pay anything until the vehicle is delivered.” Says Karen Hendry, Senior Benefits Manager. “I’ve watched employees go through the process, and I’m excited to have just taken ownership of a car myself through the programme!”

In addition to a competitive monthly payment, the program also eliminates the need for down payments, dealer fees, maintenance, or separate insurance fees as the offering is all inclusive. Stephen shared more on his recent experience by adding “I recently got a scratch on the car, so it’s been in the shop to get repaired. All I had to do was reach out to our vendor, and they got me in touch with a repair shop and coordinated everything for me”.

“As a benefits team, we are always evaluating our offerings and looking for ways to bring value to our employees through unique programmes. It’s exciting to see something new like this take off successfully in Belfast”

Learn more about Rapid7 in Belfast here.

Proactive Visibility Is Foundational to Strong Cybersecurity

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/30/proactive-visibility-is-foundational-to-strong-cybersecurity/

Proactive Visibility Is Foundational to Strong Cybersecurity

Authored by Guest IDC Blogger: Michelle Abraham

Exposures are more than CVEs, so organizations need to move beyond the traditional thinking of vulnerability management to a holistic view. Part of that view must be greater visibility into devices, users, applications, and all the digital infrastructure connected to an organization’s environment. Gaps in that view create risk exposure. Organizations must proactively identify anything that presents a risk to determine whether to act.

Solutions that improve visibility discover assets, aggregate all asset data in one place, and enrich that data to understand the relationships between users, assets, and applications. These cybersecurity asset management systems connect to other security tools in the IT environment to gather their telemetry on what they see and the communications they have. The data from these connections can overlap and be duplicative, so the system needs to deduplicate the data to render it useful for security.

Attack surface management (ASM) adds to the visibility by showing an external view of the digital estate, allowing security teams to see the view attackers have from outside their environment. Attack surfaces have expanded rapidly and often involve a hybrid multicloud environment and SaaS applications, including GenAI. Identifying unknown internet-exposed assets that provide a pathway to critical data is essential to managing risk.

Knowing what constitutes the environment that must be secured should be the foundation upon which the rest is built. Finding part of shadow IT helps with a portion of the problem but does not solve it. Alternatively, investigating assets that are falsely attributed to an organization wastes time. It is common for organizations to find 15%–30% more assets when they adopt security tooling for asset discovery.

Solutions need to bring together many sources of data — both first- and-third-party internal and external views of the environment — for a single source of truth about an organization’s digital estate. The assets must include both cloud and on-premises resources to optimize the organization’s security posture for its risk tolerance level. Solutions should also be capable of discovering unknown users and the unsanctioned use of IT resources and applications, which are additional risk exposures. The addition of threat and vulnerability intelligence helps security team’s understand the exploitability of the exposure so the most critical issues can be prioritized for remediation.

The flow of information from these tools requires continuous updating because threat actors can seize on any gap, whether recent or present from the beginning. The data shown should include asset configuration and asset criticality in the context of the business, such as whether the asset supports key business applications or has access to sensitive datasets. Knowing who owns an asset is also vital information so that security and IT know who is responsible for fixing a problem when it arises, particularly if ownership resides outside these two areas. Asset ownership will drive accountability for remediation programs and campaigns.

With a bi-directional connection to the configuration management database (CMDB), a solution that combines Cyber Asset Attack Surface Management (CAASM) and ASM further aligns the entire organization with the most updated information. It augments the CMDB to help with asset lifecycle management because end-of-life devices that no longer receive updates pose a risk. Systems should also be able to track and report on additional exposures, such as expiring certificates or unknown certificate issuers.

A map of asset and user relationships helps visualize the paths that attackers can take to traverse the network for lateral movement in the environment to get to the organization’s crown jewels. CAASM and ASM output must be more than just a dump of data from various tools; the data must be easy to query, with actionable insights that help the organization reduce risk. Matching the data from assets provides teams reacting to threats with complete context regarding assets to aid their investigation and remediation efforts. The remediation process is easier when there are recommended actions as well as integrations with ticketing systems or automation platforms that inform asset owners of issues as well as track the status of the patch or mitigation.

Consider CAASM and ASM as foundational elements to a strong, mature security program that is aware of its entire digital estate. This visibility eliminates one of the ways attackers take organizations by surprise, thereby reducing overall risk.

Message from the Sponsor

The dynamic nature of modern IT environments demands a proactive and continuous approach to exposure management. Doing so requires real-time visibility into your entire digital estate and the exposures that leave your organization vulnerable to compromise. By enriching unified internal and external views of your attack surface with real-world threat intelligence and context from your entire tooling ecosystem, teams have the situational awareness needed to prioritize response efforts and accelerate mean time to remediation. Watch this on-demand demo to learn how Rapid7 Exposure Command can help transform your security program and allow you to take command of your attack surface.

Multiple Vulnerabilities in Common Unix Printing System (CUPS)

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/26/etr-multiple-vulnerabilities-in-common-unix-printing-system-cups/

Multiple Vulnerabilities in Common Unix Printing System (CUPS)

On Thursday, September 26, 2024, a security researcher publicly disclosed several vulnerabilities affecting different components of OpenPrinting’s CUPS (Common Unix Printing System). CUPS is a popular IPP-based open-source printing system primarily (but not only) for Linux and UNIX-like operating systems. According to the researcher, a successful exploit chain allows remote unauthenticated attackers to replace existing printers’ IPP URLs with malicious URLs, resulting in arbitrary command execution when a print job is started from the target device.

The vulnerabilities disclosed by the researcher are:

  • CVE-2024-47176: Affects cups-browsed <= 2.0.1. The service binds on UDP *:631, trusting any packet from any source to trigger a Get-Printer-Attributes IPP request to an attacker-controlled URL.
  • CVE-2024-47076: Affects libcupsfilters <= 2.1b1. cfGetPrinterAttributes5 does not validate or sanitize the IPP attributes returned from an IPP server, providing attacker-controlled data to the rest of the CUPS system.
  • CVE-2024-47175: Affects libppd <= 2.1b1. The ppdCreatePPDFromIPP2 API does not validate or sanitize the IPP attributes when writing them to a temporary PPD file, allowing the injection of attacker-controlled data in the resulting PPD.
  • CVE-2024-47177: Affects cups-filters <= 2.0.1. The foomatic-rip filter allows arbitrary command execution via the FoomaticRIPCommandLine PPD parameter.

According to the researcher’s disclosure blog, affected systems are exploitable from the public internet, or across network segments, if UDP port 631 is exposed and the vulnerable service is listening. CUPS is enabled by default on most popular Linux distributions, but exploitability may vary across implementations. As of 6 PM ET on Thursday, September 26, Red Hat has an advisory available noting that they consider this group of vulnerabilities of Important severity rather than Critical.

Mitigation guidance

We expect patches and remediation guidance to be forthcoming from affected vendors and distributions over the next few days. While the vulnerabilities are not known to be exploited in the wild at time of disclosure, technical details were leaked before the issues were released publicly, which may mean attackers and researchers have had opportunity to develop exploit code. We advise applying patches and/or mitigations as soon as they are available as a precaution, even if exploitability is more limited in some implementations.

Additional mitigation guidance:

  • Disable and remove the cups-browsed service if it is not necessary
  • Block or restrict traffic to UDP port 631

Rapid7 customers

InsightVM and Nexpose customers will be able to assess their exposure to these CVEs with authenticated checks that look for affected CUPS packages on UNIX-based systems. These checks are expected to be released in a second content release this evening (ETA 10 PM ET on Thursday, September 26).

We expect to update with additional checks in the coming days as vendors release fixes and more information.

Rapid7 Recognized in Forrester’s 2024 Attack Surface Management (ASM) Wave Report

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/24/rapid7-recognized-in-forresters-2024-attack-surface-management-asm-wave-report/

Rapid7 Recognized in Forrester’s 2024 Attack Surface Management (ASM) Wave Report

This week, Rapid7 was recognized as a Contender in Forrester’s 2024 Attack Surface Management (ASM) Wave report. We’re proud to have been selected for inclusion in the report, reflecting a continued dedication to enabling customers to monitor 100% of their attack surface in real-time, and proactively mitigating exposures that leave their organizations susceptible to compromise.

Since Forrester’s initial assessment earlier this year, we’ve further extended our investments in this space, announcing the acquisition of Noetic Cyber, a market-leading cyber asset attack surface management (CAASM) vendor, and subsequently launching the Command Platform with attack surface management – and our new Surface Command product – as the foundation.

Modern business dynamics and an ever-evolving threat landscape makes successful data management a daunting challenge. This leads to a majority of organizations not having a strong grasp on their true attack surface.

  • Teams have accumulated numerous point solutions to try to keep pace with business growth and adapt to their changing environment.
  • Practitioners are consumed by assuming the role of a system integrator, trying to connect a myriad of different solutions that were never intended to be interoperable.
  • This lack of connectivity makes it impossible to get the context and clarity needed to actually make sense of data, know what to prioritize, and where to focus.

Attackers are able to exploit this data sprawl – lurking in mountains of data and betting on your inability to detect them and identify the insights that matter before it’s too late. We recognize that teams need a new path forward, and we are excited to support our customers through this next era of security with our Command Platform.

Establishing A Strong Foundation to Transform Vulnerability Management into a Proactive, Continuous Exposure Management Process

As cyber threats continue to grow in complexity, the traditional approach to Vulnerability Management (VM) must evolve. Static scanning and isolated patching efforts are no longer sufficient in the face of sophisticated attackers who exploit even the smallest gaps in security. Organizations need to adopt a more dynamic, integrated approach to exposure management – one that is continuous, context-aware, and capable of adapting to the sprawling attack surface and shifting threat landscape.

Rapid7 is uniquely positioned to support your organization’s evolution toward a more holistic and continuous process designed to continuously assess, prioritize, and remediate threats across an organization’s entire attack surface. Surface Command is built to provide the comprehensive visibility and actionable insights necessary for effective threat exposure management. Integrating data from across your entire environment – whether it’s on-premises, in the cloud, or somewhere in between – customers are able to see and understand risks in their full context.

With Rapid7, you’re not just getting another vulnerability or attack surface management tool; you’re gaining a partner that helps you elevate your entire security strategy. Our platform’s ability to aggregate and correlate data from different data sources ensures you have a complete, accurate picture of your threat landscape that you can trust. Moreover, our advanced querying capabilities allow you to quickly identify and focus on the most critical risks, enabling timely and precise remediation efforts.

Surface Command stands out in a few ways:

  • Unified Internal and External Attack Surface Visibility: Monitor your attack surface from the inside out with a dynamic asset and identity inventory alongside continuous external scans that provide an adversary’s perspective.
  • Vendor Agnostic Approach: Aggregate all data from your internal and external environments as well as your entire technology ecosystem into a unified asset model.
  • Powerful Search and Analytics: Slice and dice your data however you see fit, with powerful querying capabilities that help you find the needle in the haystack.
  • Seamless Integration and Remediation Workflows: Quickly get relevant asset insights, risk context and initiate remediation workflows all from one place.

This comprehensive visibility and contextual prioritization empowers your security team to shift from a reactive to a proactive posture, transforming your vulnerability management program into a robust, continuous defense mechanism.

Proactively Mitigate Exposures from Endpoint to Cloud

Exposure Command builds off the complete environment visibility powered by Surface Command – ingesting high-fidelity asset data from proprietary and third-party sources, automatically aggregating and correlating that data into an up-to-date asset inventory and topology map. Our powerful querying capabilities allow you to easily adjust your scope and drill into the details you need to spot control gaps, non-compliance and extinguish risk across your hybrid environment.

The platform goes beyond monitoring and asset inventory mapping, enriching telemetry with compliance and risk findings from Rapid7’s entire set of exposure management capabilities. With  hybrid vulnerability management, comprehensive cloud security, and web application testing in one complete solution, security teams can shift from reactive to proactive to stay ahead of adversaries.

Exposure Command extends the power of Surface Command with:

  • Pinpoint and Mitigate Vulnerabilities Everywhere: Automatically prioritize vulnerabilities across your hybrid environment based on exploitability and potential impact.
  • Monitor Effective Access and Enforce Least Privilege Access: Analyze all roles and identities across your clouds to help eliminate excessive permissions and enforce LPA at scale.
  • Proactively Mitigate Exposures in Cloud-native Apps: Avoid risk before it reaches production with IaC and web app scanning that gives actionable feedback to devs where they work.
  • Spot Avenues for Attackers to Traverse Your Cloud Network: Visualize interconnected resources and uncover paths for attackers to move laterally across your environment with attack path analysis.

With these powerful capabilities, Exposure Command allows teams to continuously assess their attack surface, validate exposures and confidently take action with remediation guidance that takes into account existing downstream controls and the blast radius of a potential compromise.

Interested in Learning More About Exposure Command?

If you’re interested in diving deeper into how Rapid7 can help transform your security operations, be sure to check out our recent webcast with Jon Schipp, Sr Dir. Product Management, and Thomas Green, Sr Security Solutions Engineer during which they discuss key strategies for leveraging Exposure Command to stay ahead of today’s evolving threats.

Three Recommendations for Creating a Risk-Based Detection and Response Program

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/24/three-recommendations-for-creating-a-risk-based-detection-and-response-program/

Three Recommendations for Creating a Risk-Based Detection and Response Program

It should come as little surprise to most security professionals that keeping pace with the evolution of threat actors has become harder and harder. Maintaining visibility into the threat landscape and on top of external risk vectors is more than a matter of incorporating more point solutions. It takes a concerted risk-based approach, where the tools you choose are just one leg of the tripod.

In a report released earlier this summer, Gartner analysts offer three recommendations for fostering an environment of risk-based threat detection, investigation, and response that includes a deeper understanding of your organization’s risk profile by more than just the security team. Below are our three main takeaways from the Gartner® 3 Ways to Apply a Risk-Based Approach to Threat Detection, Investigation, and Response.

Takeaway 1: Better alignment and clearer objectives

The need to break silos between teams is a time-honored proposition that holds even more weight now than it ever has. Gartner suggests creating a quorum of business leaders from across the entire organization to be read into the state of your security and the needs going forward. Prioritize accurate and regular reporting of security metrics to build trust and create a consistent atmosphere of effective transparency. This group should be diverse, with decision makers and specialists from core departments. According to Gartner, the goal should be to:

“Allow the business to be part of the conversation and therefore champions of the capability, elevating the security program to a business function rather than an I&O underpinning.”

Takeaway 2: Integrated risk context

Giving incident responders as much information (and the right information) they need to quickly and efficiently respond to threats requires a complex layering of risk information that includes prioritization for the businesses key assets. Gartner recommends the use of cyber-risk information elements directly implemented into an IR program, layering in asset-based and business-risk information that gives responders the context they require to appropriately triage what can often be a large volume of data.

Gartner says:

“Incident responders should have as much information at their disposal as needed to be effective at finding a needle in a haystack.”

Takeaway 3: Fully enriched business context from jump

Too much information can often be as detrimental to a security team as too little. SecOps needs to have access to the right information in the most efficient way possible in order to find the signal through the noise. Gartner recommends reducing investigative delays through enriched information complete with business context (see, they are all connected). This transparency can be accomplished in part through SIEM, CAASM, and threat intelligence tools and a robust vulnerability management program, but it is worth noting that Gartner prioritizes providing the right information, not the most information; hence, utilizing the right tools.

All three of these recommendations combine to create a risk-based approach to detection, investigation, and response that Gartner says: “…organizations can expect to create measurable efficiency gains in threat detection and increase their ability to respond to threats in a timely manner.”

The Gartner® 3 Ways to Apply a Risk-Based Approach to Threat Detection, Investigation, and Response, report goes into even greater detail on the best approaches for implementing a risk-based approach to D&R.

Download the report here.

Gartner, 3 Ways to Apply a Risk-Based Approach to Threat Detection, Investigation and

Response, Jonathan Nunez ,  Pete Shoard , 10 July 2024.

GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the

U.S. and internationally and is used herein with permission. All rights reserved.

High-risk vulnerabilities in common enterprise technologies

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/19/etr-high-risk-vulnerabilities-in-common-enterprise-technologies/

High-risk vulnerabilities in common enterprise technologies

Rapid7 is warning customers about several high-risk vulnerabilities in common enterprise technologies that are attractive potential attack targets for both state-sponsored and financially motivated adversaries. We are advising customers to prioritize remediation for these issues on an expedited basis wherever possible:

  • CVE-2024-41874: Critical remote code execution vulnerability in Adobe ColdFusion
  • CVE-2024-38812, CVE-2024-38813: Remote code execution and privilege escalation vulnerabilities (respectively) in Broadcom VMware vCenter Server and Cloud Foundation
  • CVE-2024-29847: Critical remote code execution (via deserialization) vulnerability in Ivanti Endpoint Manager (EPM)

Adobe ColdFusion CVE-2024-41874

On September 10, 2024, Adobe published a critical advisory for CVE-2024-41874, an unauthenticated remote code execution issue that occurs as a result of unsafe Web Distributed Data eXchange (“Wddx”) packet deserialization. Rapid7 MDR has previously observed exploitation that targets Wddx for remote code execution; we have also previously observed exploitation of multiple other ColdFusion CVEs.

Affected products and mitigation: Adobe ColdFusion 2023 (update 9 and earlier) and Adobe ColdFusion 2021 (update 15 and earlier) are vulnerable to CVE-2024-41874. The vulnerability is resolved in versions 10 and 16, respectively. For more information, see the vendor advisory.

Broadcom VMware vCenter Server CVEs

On September 17, 2024, Broadcom published an advisory on CVE-2024-38812, a critical heap overflow vulnerability affecting VMware vCenter Server. Successful exploitation of CVE-2024-38812 allows an attacker with network access to the vulnerable server to execute code remotely on the target system. CVE-2024-38813, a local privilege escalation vulnerability, was also reported by the same researchers, making this a full-chain exploit. We are not aware of exploitation in the wild as of September 19, 2024, but vCenter Server is a high-value attack target for ransomware and extortion groups.

Affected products and mitigation: Broadcom VMware vCenter Server 7.0 and 8.0 are vulnerable to CVE-2024-38812 and CVE-2024-38813. Fixes are available as indicated in the vendor advisory. Broadcom also has an FAQ available.

Ivanti Endpoint Manager CVE-2024-29847

On September 10, 2024, Ivanti published a security advisory on CVE-2024-29847, an unsafe deserialization vulnerability in Ivanti Endpoint Manager (EPM) solution. Successful exploitation allows unauthenticated attackers to execute code remotely on target systems. Vulnerability details and proof-of-concept exploit code are available.

Affected products and mitigation: Ivanti Endpoint Manager (EPM) 2022 SU5 (and earlier) and EPM 2024 are vulnerable to CVE-2024-29847. Customers using EPM 2022 can remediate this and other recent vulnerabilities by updating to 2022 SU 6. Per Ivanti’s security advisory, EPM 2024 customers can apply an available security patch while waiting for 2024 SU1, which is yet to be released. See Ivanti’s advisory for the latest information.

Rapid7 customers

InsightVM and Nexpose customers can assess their exposure to Adobe ColdFusion CVE-2024-41874 and Broadcom VMware vCenter Server CVE-2024-28812 and CVE-2024-38813 with vulnerability checks released previously. A vulnerability check for Ivanti EPM CVE-2024-29847 is in development and is expected to be available in tomorrow’s (Friday, September 20) content release.

The Growing Importance of Exposure Management: Our Key Insights from Gartner® Hype Cycle™ for Security Operations, 2024

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/13/the-growing-importance-of-exposure-management-our-key-insights-from-gartner-r-hype-cycle-for-security-operations-2024/

The Growing Importance of Exposure Management: Our Key Insights from Gartner® Hype Cycle™ for Security Operations, 2024

The Gartner® Hype Cycle™ for Security Operations, 2024  was published in late July, and is an interesting look at the dynamic nature of both the threat landscape and the diverse range of technologies that security & risk management (SRM) professionals use to safeguard their organizations.

Understanding the Hype Cycle

Gartner Hype Cycles provide a graphic representation of the maturity and adoption of technologies and applications, and how they are potentially relevant to solving real business problems and exploiting new opportunities. Over 90 Hype Cycles are published per year. Hype Cycles provide a snapshot of the relative market penetration, maturity and benefit of innovations within a certain segment, such as a technology area or business market. This Hype Cycle helps security and risk management leaders strategize and deliver SecOps capability and functions.

What we think are key themes from this year’s Hype Cycle for SecOps

The 2024 Hype Cycle has seen some notable additions and consolidations, particularly around the rapidly-evolving Threat Exposure Management (TEM) market, as existing vulnerability assessment and management approaches mature to support the Continuous Threat Exposure Management (CTEM) framework. In the report Gartner defines CTEM as “a program helping organizations to improve their maturity when they govern and operationalize the five recommended phases of exposure management: scoping, discovery, prioritization, validation and mobilization.’”

Three new profiles reflect this evolution:

  • Threat Exposure Management – This is intended to help organizations answer the question, “ow exposed are we?” It extends traditional approaches to vulnerability management to focus on risk reduction across a much wider potential attack surface, including cloud, SaaS applications and the third-party supply chain.

    Today,many organizations currently have a siloed approach to exposure management across many different domains — external, vulnerability scanning, penetration testing — and are struggling to keep up with the pace of environmental change.

    Gartner rates the potential benefit of Threat Exposure Management as ‘transformational’ and states that organizations should ‘employ proper governance and repeatability to make their threat exposure management programs continuous.’

  • Exposure assessment platforms (EAPs) – This is a new category with a ‘high’ benefit rating from Gartner. In the report, Gartner states that EAPs ‘continuously identify and prioritize exposures, such as vulnerabilities and misconfigurations, across a broad range of asset classes. They natively deliver or integrate with discovery capabilities, such as assessment tools that enumerate exposures like vulnerabilities and configuration issues, to increase visibility.’

    Gartner has removed both vulnerability assessment (VA) and vulnerability prioritization technologies (VPT) from this year’s Hype Cycle, stating that they have been ‘subsumed into exposure assessment platforms.’

    We believe that a potential benefit of EAPs is to provide better insights into high-risk exposures, which could allow organizations to prevent security incidents and breaches. They can also improve operational efficiency by providing centralized visibility of assets and exposures, supporting risk scoring reporting and trend analysis across the organization.

    Rapid7 is named as a Sample Vendor for EAP in this latest report.

  • Adversarial exposure validation – The third new category related to exposure management covers the validation pillar of a CTEM program. As noted in the report, “Adversarial exposure validation technologies offer offensive security technologies simulating threat actor tactics, techniques, and procedures to validate the existence of exploitable exposures and test security control effectiveness. Within this profile, Gartner has consolidated breach attack simulation and autonomous penetration testing and red teaming. “
    Gartner recommends that security and risk leaders should ‘Integrate existing attack simulation and penetration testing scenarios into an adversarial exposure validation roadmap, as part of a shift from vulnerability management to a CTEM program.’

As well as these new categories, we also see movement among some of the existing technologies that can support CTEM initiatives – notably Cyber Asset Attack Surface Management (CAASM), External Attack Surface Management (EASM) and Digital Risk Protection Services (DRPS).

Both EASM and DRPS are in the ‘Trough of Disillusionment’ on this year’s Hype Cycle.  Gartner notes, “SRM leaders are reevaluating the value they’re getting from technologies in the trough, often having to reinforce their justification for budgets. For example:[…] Enterprises were unprepared to consume and operationalize service output (digital risk protection services, external attack surface management, ITDR).

CAASM has moved from ‘Innovation Trigger’ to the ‘Peak of Inflated Expectations’, reflecting the growing demand from enterprises to gain better visibility of their attack surfaces. CAASM helps provide more comprehensive visibility into assets by consolidating asset and exposure information into a holistic view. Noetic Cyber, a recent acquisition of Rapid7, is also a Sample Vendor for CAASM.

Rapid7’s vision for Exposure Management

Rapid7 recently announced the availability of Exposure Command and Surface Command, the first two solutions launched on the new Command Platform. Surface Command provides 360-degree visibility across the internal and external environment by bringing together EASM and CAASM in a single solution, enabling security teams to view and prioritize high-risk assets across their extended environments.

Building on the unparalleled visibility provided by Surface Command, Exposure Command expands traditional vulnerability management programs with insights and context from vulnerability, cloud and application security tools, establishing a single, consolidated platform for exposure management across the organization.

The Growing Importance of Exposure Management: Our Key Insights from Gartner® Hype Cycle™ for Security Operations, 2024

This centralized point of exposure management allows security leaders to prioritize based on the overall risk to the business, understand complex attack paths across the cloud and on-premise environments, and surface the top areas teams need to focus on and while elevating the mitigation activities that would have the largest impact in reducing the overall risk score of your environment.

We believe that these new capabilities align well with the Gartner concept of exposure assessment platforms and the overall requirements of a threat exposure management program. To understand more about Rapid7’s approach to attack surface and exposure management, you can find out more here.

Gartner, Hype Cycle for Security Operations, 2024, July 2024.
GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally, and HYPE CYCLE is a registered trademark of Gartner, Inc. and/or its affiliates and are used herein with permission. All rights reserved.
Gartner does not endorse any vendor, product or service depicted in its research publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner’s research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.

CVE-2024-40766: Critical Improper Access Control Vulnerability Affecting SonicWall Devices

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/09/etr-cve-2024-40766-critical-improper-access-control-vulnerability-affecting-sonicwall-devices/

CVE-2024-40766: Critical Improper Access Control Vulnerability Affecting SonicWall Devices

On August 22, 2024, security firm SonicWall published an advisory on CVE-2024-40766, a critical improper access control vulnerability affecting SonicOS, the operating system that runs on the company’s physical and virtual firewalls. While CVE-2024-40766 was not known to be exploited in the wild at the time it was initially disclosed, the SonicWall advisory was later updated to note that “this vulnerability is potentially being exploited in the wild.”

As of September 9, 2024, Rapid7 is aware of several recent incidents (both external and Rapid7-observed) in which SonicWall SSLVPN accounts were targeted or compromised, including by ransomware groups; evidence linking CVE-2024-40766 to these incidents is still circumstantial, but given adversary interest in the software in general, Rapid7 strongly recommends remediating on an emergency basis. Vulnerabilities like CVE-2024-40766 are frequently used for initial access to victim environments.

SonicWall’s advisory indicates CVE-2024-40766 is an improper access control vulnerability “in the SonicWall SonicOS management access and SSLVPN, potentially leading to unauthorized resource access and in specific conditions, causing the firewall to crash.” The vulnerability was added to the U.S. Cybersecurity and Infrastructure Security Agency’s (CISA) list of known exploited vulnerabilities (KEV) on September 9, 2024.

Mitigation guidance

Per the vendor advisory, CVE-2024-40766 affects SonicWall Gen 5 and Gen 6 devices, as well as Gen 7 devices running SonicOS 7.0.1-5035 and older versions.

Affected versions and platforms include:

  • SOHO (Gen 5): 5.9.2.14-12o and older versions affected
  • Gen6 Firewalls: 6.5.4.14-109n and older versions affected (see the advisory for a full list of affected devices)
  • Gen7 Firewalls: SonicOS build version 7.0.1-5035 and older versions affected, but SonicWall recommends installing the latest firmware (see the advisory for a full list of affected devices)

SonicWall recommends restricting firewall management access to trusted sources and/or ensuring firewall WAN management is not accessible from the public internet. They similarly recommend that SSLVPN access is limited to trusted sources, and/or disabling SSLVPN access from the internet.

Rapid7 customers

Our InsightVM engineering team is investigating options for coverage of CVE-2024-40766. We will update this blog with further information no later than 10 AM ET on Tuesday, September 10.

Multiple Vulnerabilities in Veeam Backup & Replication

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/09/etr-multiple-vulnerabilities-in-veeam-backup-and-replication/

Multiple Vulnerabilities in Veeam Backup & Replication

On Wednesday, September 4, 2024, backup and recovery software provider Veeam released their September security bulletin disclosing various vulnerabilities in Veeam products. One of the higher-severity vulnerabilities included in the bulletin is CVE-2024-40711, a critical unauthenticated remote code execution issue affecting Veeam’s popular Backup & Replication solution. Notably, upon initial disclosure, the Veeam advisory listed the CVSS score for CVE-2024-40711 as “high” rather than “critical” — as of Monday, September 9, however, the CVSS score is listed as 9.8, which confirms exploitation is fully unauthenticated.

Five other CVEs were also disclosed in Backup & Replication, including several that allow users who have been assigned low-privileged roles to alter multi-factor authentication (MFA) settings, achieve remote code execution as a service account, and extract sensitive data (e.g., credentials, passwords). Other vulnerabilities in the bulletin affect additional Veeam offerings — notably, there are also two critical vulnerabilities in Veeam Service Provider Console.

While CVE-2024-40711 has received attention from security media and community members, we are not aware of any known exploitation as of Monday, September 9, 2024. Veeam Backup & Replication has a large deployment footprint, however, and several previous vulnerabilities affecting the software have been exploited in the wild, including by ransomware groups. It is possible that one or more of these vulnerabilities may be used to facilitate extortion attacks. More than 20% of Rapid7 incident response cases in 2024 so far have involved Veeam being accessed or exploited in some manner, typically once an adversary has already established a foothold in the target environment.

Mitigation guidance

The following vulnerabilities affect Veeam Backup & Replication 12.1.2.172 and all earlier version 12 builds, per the vendor advisory:

  • CVE-2024-40711: Unauthenticated remote code execution (CVSS 9.8)
  • CVE-2024-40713: Allows a low-privileged user to alter MFA settings and bypass MFA (CVSS 8.8)
  • CVE-2024-40710: Covers multiple issues, per the advisory, including one that allows for remote code execution as the service account and enables extraction of saved credentials and passwords (CVSS 8.8)
  • CVE-2024-39718: Allows a low-privileged user to remotely remove files on the system with permissions equivalent to those of the service account (CVSS 8.1)
  • CVE-2024-40714: A vulnerability in TLS certificate validation allows an attacker on the same network to intercept sensitive credentials during restore operations (CVSS 8.3)
  • CVE-2024-40712: A path traversal vulnerability allows an attacker with a low-privileged account and local access to the system to perform local privilege escalation (CVSS 7.8)

Veeam Backup & Replication customers should update to the latest version of the software (12.2 build 12.2.0.334) immediately, without waiting for a regular patch cycle to occur. Unsupported software versions were not tested but, per the vendor, should be considered vulnerable.

Other CVEs in Veeam’s September 4 security bulletin affect Veeam Agent for Linux, Veeam ONE, Veeam Service Provider Console, Veeam Backup for Nutanix AHV, and Veeam Backup for Oracle Linux Virtualization Manager and Red Hat Virtualization.

Rapid7 customers

InsightVM and Nexpose customers will be able to assess their exposure to the Veeam Backup & Replication CVEs listed in this blog with vulnerability checks expected to be available in today’s (Monday, September 9) content release.

Our 4 Essential Strategy Takeaways from the Gartner® 2024 Report – How to Prepare for Ransomware Attacks

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/09/our-4-essential-strategy-takeaways-from-the-gartner-r-2024-report-how-to-prepare-for-ransomware-attacks/

Our 4 Essential Strategy Takeaways  from the Gartner® 2024 Report – How to Prepare  for Ransomware Attacks

As ransomware threats continue to evolve, security and risk management leaders must stay ahead by adopting comprehensive strategies to protect their organizations. The 2024 Gartner report, “How to Prepare for Ransomware Attacks”, provides critical insights into the latest tactics used by bad actors and offers practical solutions on how to fortify defenses.

Below, we highlight our four key strategy takeaways  from the report to help your organization prepare for and respond to ransomware attacks.

Adapt to the rise of extortionware

Traditional ransomware tactics are shifting towards extortionware—where attackers steal data and demand payment for its destruction rather than encrypting it. This growing threat emphasizes the need for robust data protection strategies.

According to Gartner: “Extortionware (encryption-free, data theft attack) is a growing tactic being used by bad actors.”

This evolution in tactics, which includes the emergence of 21 new ransomware groups in the first half of 2024, as noted in Rapid7’s Ransomware Radar Report, underscores the need for organizations to continuously update their defenses to counter new threats.

Actionable Strategy: Regularly update your threat models and security measures to account for new and emerging ransomware groups. Invest in advanced threat intelligence to stay informed about the latest tactics used by these criminal enterprises.

Strengthen your defenses with advanced detection technologies

This is increasingly important as ransomware attacks are becoming more frequent and sophisticated. Rapid7’s research highlights a 23% increase in ransomware posts on leak sites during the first half of 2024, further emphasizing the growing threat landscape.

We believe Gartner reinforces the importance of detection, stating: “… identity threat detection and response (NDR) tools  collect indicators of compromise (IOCs) and events that alert you to anomalous behaviors that could indicate that an attack ‘may’ be underway.”

In addition to these detection tools, Gartner advises that a defense strategy should include Endpoint Protection Platforms (EPPs), EDR, and mobile threat defense (MTD) solutions.

For organizations lacking the necessary in-house expertise or resources, Gartner recommends supplementing EDR with managed services: “If internal teams don’t have the necessary skill set or bandwidth, supplement EDR with managed services (see Market Guide for Managed Detection and Response Services).”

Actionable strategy: Implement and regularly update behavioral-anomaly-based detection technologies. Ensure that your security operations center (SOC) is equipped to respond swiftly to any detected threats.

Rapid7’s Managed Threat Complete, which integrates core MDR functionality with transparency into operations and technology, ensures comprehensive visibility across endpoints, networks, users, and cloud infrastructure. We believe this aligns with the Gartner recommendation to supplement EDR with managed services to enhance your organization’s security posture (see the Gartner Market Guide for Managed Detection and Response Services).

Pay attention to vulnerable targets

While large organizations are often targeted, mid-sized companies are increasingly vulnerable to ransomware attacks. Rapid7’s findings support this, showing that companies with $5 million in annual revenue are being attacked up to five times more often than larger enterprises. These organizations are particularly attractive to attackers due to their valuable data and often less mature security defenses.

Actionable strategy: Mid-sized organizations should prioritize investing in mature cybersecurity defenses, particularly in endpoint protection, identity management, and regular security training for employees.

You can view the Rapid7 Ransomware Radar Report here.

Pay attention to vulnerable targets

While large organizations are often targeted, mid-sized companies are increasingly vulnerable to ransomware attacks. Rapid7’s findings support this, showing that companies with $5 million in annual revenue are being attacked up to five times more often than larger enterprises. These organizations are particularly attractive to attackers due to their valuable data and often less mature security defenses.

Actionable strategy: Mid-sized organizations should prioritize investing in mature cybersecurity defenses, particularly in endpoint protection, identity management, and regular security training for employees.

You can view the Rapid7 Ransomware Radar Report here.

Prepare with a comprehensive ransomware playbook

One of the key insights from the Gartner research is the critical importance of having a well-prepared incident  response plan. Given the increasingly sophisticated nature of ransomware groups—many of which now operate like full-fledged businesses with their own marketplaces and support networks—a detailed and rehearsed ransomware playbook is essential for any organization.

Gartner  states: “Develop an incident response plan with containment strategies that is augmented with a ransomware playbook.”

Actionable strategy: Develop and regularly update a ransomware playbook that includes clear roles, decision-making protocols, and communication plans. Conduct regular tabletop exercises to ensure your team is prepared to act swiftly and effectively.

Conclusion: fortify your defenses against ransomware

Ransomware is an ever-present threat that requires a proactive, multi-layered approach to defense. We feel the 2024 Gartner Report “How to Prepare for Ransomware Attacks” provides essential strategies for preparing, detecting, and responding to these attacks. By implementing these recommendations, we believe your organization can better protect itself against the evolving tactics of cybercriminals.

Download the full Gartner report to explore detailed insights and recommendations for strengthening your ransomware defenses.

Gartner, Inc. How to Prepare for Ransomware Attacks. Paul Furtado. 16 April 2024.

GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the

U.S. and internationally and is used herein with permission. All rights reserved.

Preparing for Unknown Risks: How to Better Prepare for Risks You Can’t See Yet

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/08/22/preparing-for-unknown-risks-how-to-better-prepare-for-risks-you-cant-see-yet/

Preparing for Unknown Risks:
How to Better Prepare for Risks You Can't See Yet

As security professionals we’re used to dealing with unknowns and unpredictability. We understand that it’s impossible to always know what’s around the corner. It’s not just about external threats and the big breaches splashed across the news headlines. On one hand, we’re combating threat actors attempting to steal information, money or simply trying to cause havoc. On the other, we’re trying to better understand employee behaviour amidst the myriad of applications they use on a daily basis; always vigilant for any suspicious activity. And while it certainly makes our jobs interesting, unpredictability runs contrary to how the organisations we protect prefer to operate.

Predicting what’s going to happen in our cyber world is nearly impossible.  A greater challenge is explaining this to stakeholders and conveying how difficult it is to get (and stay) one step ahead of threat actors. We’re paid to understand this, yet  it can often feel like shooting in the dark when anticipating the next strike.

Senior leadership teams thrive on certainty and predictability. So how do you plan and manage this?

Focus on what you can control

Ultimately, you can only control what’s in front of you.:he tools, applications and services the business uses to operate. While this might seem obvious, many people spend a considerable amount of time and energy on things that can’t influence.

Your time is best spent focusing on what’s visible and within reach. Begin by identifying the crown jewels of your organisation — understanding the scope of your environment and what exactly you’re protecting. Then, implement controls and monitor for abnormalities.

Regularly conduct comprehensive risk assessments and vulnerability scans to identify potential weaknesses in your organisation’s IT infrastructure. This helps uncover existing vulnerabilities and potential entry points for cyber threats, particularly in areas where the ‘crown jewels’ are held!

Leverage threat modelling

Threat modelling provides very useful analysis, unique to your organisation. Various factors determine your threat model including industry, compliance and regulations and finally, customers. Using your threat model as a guide, you can get a clear picture of the unique risks your business faces and design controls around those. These insights can also inform your approach to Table Top Exercises, preparing you for potential incidents.

While predicting a threat actor’s next steps is challenging, gathering and understanding this information through these exercises can enhance your ability to anticipate future threats. Afterall, identifying unknowns is crucial.

With a clear focus on what you’re protecting, you’re now able to analyse and draw learnings from past events, which is often a good predictor of future occurrences.  While threat actors are often portrayed as volatile and unpredictable (and this is true in some cases), they’re only human – and humans are creatures of habit. Recognizing patterns in their behaviour can provide valuable insights.

This is where threat intelligence gathering is extremely useful. Make sure you stay informed about the latest cyber threats and attack trends by monitoring reputable sources of threat intelligence. Placing yourself in a position to better understand what trends and patterns have occurred in the past, may help you better predict the types of threats or vulnerabilities your organisation could be subject to in the future.

How Rapid7 can help – Threat Command

Threats can come from any direction. Rapid7’s Threat Command scans the clear, deep, and dark webs for potential dangers before they affect your organisation. It provides contextualised alerts on threats affecting your business, proactively researching malware, tactics, techniques, and procedures (TTPs), phishing scams, and other threat actors. Threat Command replaces point solutions with an all-in-one external threat intelligence, digital risk protection, indicators of compromise (IOCs) management, and remediation solution.

Find out more.

Proactive profiling

Conducting risk assessments, vulnerability scans and gathering threat intelligence helps you to understand the ‘cyber profile’ of your organisation. This preparation helps you anticipate the types of threats typically used against similar-sized organisations or those in your industry. There are trends and patterns that emerge., for example, our Ransomware Data Disclosure Report found that internal financial data was leaked 71% of the time in the healthcare and pharmaceutical sectors — more than in any other industry, including financial services.

Tailored strategies for different organisations

Threat actors focus on ‘big fish’ because they’re often  newsworthy and recognizable – threat actors have egos too! Large organisations should consider strong encryption and network segmentation to contain potential threats. Prioritise data types for additional protection.

For smaller organisations, where an online presence is critical but public profile is lower, backup and recovery are essential. This is in case  systems are locked or shut down. Ensure software and systems are up-to-date with the latest security patches to prevent threats exploiting known vulnerabilities. Automate this process to keep it off the to-do list.

Building a detailed picture of your data and crown jewels allows you to reduce risks and build cyber resilience, identifying potential unknowns along the way.

How Rapid7 can help – Managed Detection and Response

Managed Detection and Response (MDR) services accelerate your team’s incident-response capabilities with end-to-end service. Acting as a seamless extension of your team, our experts monitor your business 24/7/365.. They leverage proprietary technology and analytics to keep your business safe against advanced threats. You can also gain access to our award winning VRM technology to perform unlimited scans to your in-scope environment to spot vulnerabilities before they’re exploited by threat actors.

Find out more.

Communication is key

But don’t forget — communication is key. Organisations crave  predictability and cybersecurity can often appear to be a ‘black box’ to those unfamiliar with  it. Transparent lines of communication and regular updates means you can paint a clear picture of potential risks that could impact your business (not to mention the business benefits of investing in security).

Proactivity is essentia. With so much happening in our field, it can be tempting to simply react and respond to what’s going on around us. However, demanding weekly updates with your stakeholders and keeping them informed of your work will make managing a crisis more bearable. This way, if something unpredictable happens, it won’t be a complete surprise, and you’ll be better prepared to manage it and your senior leaders.

5 Key Insights from the Gartner® Market Guide for Cloud-Native Application Protection Platforms (CNAPP)

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/08/19/5-key-insights-from-the-gartner-r-market-guide-for-cloud-native-application-protection-platforms-cnapp/

5 Key Insights from the Gartner® Market Guide for Cloud-Native Application Protection Platforms (CNAPP)

As the cloud landscape continues to evolve, organizations face the growing challenge of securing their cloud-native applications. We feel the 2024 Gartner Market Guide for Cloud-Native Application Protection Platforms (CNAPP) provides invaluable insights into the latest trends and technologies that are reshaping how companies protect their digital assets. Below, we highlight five key takeaways from the report to help you navigate the ever-changing cloud security ecosystem.

Key takeaway 1: The expanding attack surface

The attack surface of cloud-native applications is widening, with attackers increasingly targeting runtime environments, networks, compute, storage, identities, and permissions. Misconfigurations and vulnerabilities in APIs and the software supply chain are also primary targets for cybercriminals.

According to Gartner: “CNAPP offerings bring together multiple disparate security and protection capabilities into a single platform focused on identifying and prioritizing excessive risk of the entire cloud-native application and its associated infrastructure.”

This comprehensive approach allows organizations to tackle threats head-on and maintain a secure cloud environment.

Key takeaway 2: Evolving developer responsibilities

Developers are taking on more responsibility for security as organizations embrace DevOps and shift left in their security practices. The need for advanced tools that address vulnerabilities and deploy infrastructure as code has become crucial.

The report highlights: “Proactively identifying and prioritizing risks during development, while providing developers with adequate context, is essential due to developers perceiving security as an obstacle.”

To support this shift, organizations should look for CNAPP solutions that integrate seamlessly with development processes, offering full life cycle visibility and protection.

Key takeaway 3: The importance of contextual risk analysis

Security teams must prioritize tasks and provide developers with the context needed to remediate issues quickly. Without this context, developers can become overwhelmed by alerts, leading to decreased productivity and potentially leaving vulnerabilities unaddressed.

The research suggests: “Security leaders should leverage CNAPP to strengthen defenses against attacks on network, compute, storage, identities, permissions, APIs, and the software supply chain, thereby mitigating potential risks and safeguarding critical assets.”

A strong CNAPP platform helps security teams understand the broader context of threats, making it easier to prioritize and address the most pressing issues.

Key takeaway 4: Integration and consolidation are key

The CNAPP market has experienced significant growth and consolidation, with a handful of vendors offering comprehensive platforms that integrate security across development and operations.

We believe the report emphasizes the benefits of consolidation: “CNAPP reduces operational complexity through consolidation of vendors, consoles, policies, and contracts, thereby reducing the chances of misconfiguration or mistakes.”

Organizations are moving toward unified solutions that offer consistent security policies across all application components, from code to containers to virtual machines. This integration not only simplifies management but also enhances security posture across cloud environments.

Key takeaway 5: Visualizing interconnected relationships

Understanding the relationships between various components of cloud-native applications is crucial for effective security. CNAPPs should leverage graph database technology to map these interconnected relationships, providing a visual representation of how resources, identities, and application components interact.

The report states: “A deep understanding of the relationships between an application’s elements (VMs, containers, service functions and storage), security posture, permissions, and connectivity, typically enabled by underlying graph database technology.”

This visualization is more than just a nice-to-have; it is becoming an expected feature. By using graph technology, CNAPP platforms can show potential paths for attackers to move laterally within an environment, enabling security teams to prioritize risks more effectively and understand the potential blast radius of a compromise. Rapid7’s latest Exposure Command, for example, incorporates this advanced graph visualization technology and attack path analysis, helping teams gain deeper insights into their security posture and enhance their threat mitigation strategies.

Conclusion: Navigating the cloud security landscape

Securing cloud-native applications requires a comprehensive and integrated approach that addresses risks throughout the development and production lifecycle. We feel the Gartner Market Guide for CNAPPs highlights the importance of selecting solutions that offer robust security features, seamless integration, and actionable insights to help organizations protect their digital assets effectively.

Download the full Gartner Market Guide for Cloud-Native Application Protection Platforms to explore how CNAPPs can enhance your cloud security strategy and keep your applications safe from emerging threats.

Brandon Adkins’ Career Journey – Taking Chances and Tackling New Challenges

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/08/15/brandon-adkins-career-journey-taking-chances-and-tackling-new-challenges/

Brandon Adkins’ Career Journey - Taking Chances and Tackling New Challenges

Brandon Adkins is the Manager of our Threat Intelligence & Detection Engineering (TIDE) team. His career journey spans a variety of roles and teams where he has been able to showcase his technical skills in security. Since joining Rapid7, he’s had experience as a Penetration Testing Consultant, working with both red and purple teams, and now as a leader with our TIDE team he supports engineers in writing effective detections for products like Insight IDR.

Adkins is no stranger to seeking out and taking on new technical challenges. Before joining Rapid7, he had built a long and successful career, achieving the role of Principal Information Security Analyst.

“I decided to come to Rapid7 because I was at a point in my career where in order to advance further, I was either going to be a people manager, or I would have to look elsewhere,” said Adkins. “At the time, I didn’t feel like I was ready to hang up my hat as an individual contributor. I still felt I had more to offer on the technical side, and didn’t want to be done yet.”

This drive led him to pursue his Offensive Security Certified Professional (OSCP) designation, enabling him to become a Penetration Tester. “I got my notification that I had passed my test the day I had my first interview with Rapid7. So the fact that I got the job really shows how they were willing to take a risk on someone brand new, and invest in my career by giving me that chance.”

When asked what the biggest shift was in coming to Rapid7, he praises the quality and caliber of talent he was exposed to. “In my past role, I was used to being one of the smartest guys in the room. Coming into Rapid7 and seeing the depth of knowledge that is here on the team, and the level of expertise everyone brings, I very quickly realized that there was so much more for me to learn.”

Adkins was inspired by those around him, and his curiosity and desire to keep growing didn’t stay quiet for long. During his time, he moved from red teams to purple teams, and ultimately started to become curious about the detection engineering team who is responsible for ensuring our products are effectively able to identify suspicious behavior.

“I really enjoyed my time as a pen tester. I loved purple teaming because I got to work alongside our customer security teams and help them identify ways to improve.” This collaborative experience and being able to blend his experience from blue and red teaming sparked further curiosity in detection engineering.

“I reached out to a few people and thought my next move might be to join the team as an engineer. When we actually got to talking, it turns out what the team really needed at the time was a manager. I was hesitant at first, but the more that I thought about it the more I thought, ‘I think I can really help make a difference here and do something good.’”

Adkins’ extensive technical background combined with his ability to work collaboratively in a customer-facing capacity ended up being the combination of talent that was needed to help the team work more efficiently. “They already have great people writing code. What they needed, and what I hope to bring, is someone who can speak to the business and advocate for the team, to smooth out any speed bumps, and ultimately clear the way so they can do what they are best at”.

Since taking on his new role in January 2024, the team has grown to be three times the size it was originally. “It’s an exciting time to be part of the team because we are getting the support and investment from the business to continue to iterate and make our products even better.”

As he continues to hire new people into the business, and support existing employees in growing their careers, Adkins says there are two key factors he looks for to spot high-caliber talent – communication skills, and the ability to collaborate.  “Technical ability is obviously important, you have to be able to do the work. But beyond that, if we’re looking for someone to step into a more senior role on the team, or evaluate if someone is ready for a promotion, I want to see examples of how they can communicate their ideas and challenges effectively, and how they use the partnerships we have across the business to collaborate and find solutions.”

For the TIDE team, Rapid7’s engineers sit at the intersection of customer feedback, product management, and our security operations center. “At a certain point, we can’t do our jobs well without having a partnership with other teams. We need to know from the SOC team if something isn’t working the way it should be. We want to know from our customers and Customer Advisors what’s working well and what more they’d like to see, and we need to work alongside our product teams and analysts to understand and synthesize data to get a full picture of the customer attack surface.”

For Adkins, his journey in cybersecurity is one that has opened a number of different doors as he’s explored new roles and teams. His expertise and experience has helped support customers around the world in understanding their attack surface and more efficiently protecting their business from bad actors.

When asked what advice he would share for others looking to grow their career, he shared “When you get an opportunity to try something new – especially at Rapid7 – jump at it. Rapid7 hired me as a pen tester with zero pentest experience. Four years later, they took a risk on me again as a people leader with zero previous people leader experience. This is a place where these moves and opportunities are not only available, but are supported by the leadership around you. If you have the fundamental skills necessary and it’s something you’re interested in, there’s a ton of room for you to expand your career.”

Rapid7 Introduces Exposure Command to Eliminate the Security Visibility Gap

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/08/05/rapid7-introduces-exposure-command-to-eliminate-the-security-visibility-gap/

Exposure Command provides 360-degree visibility and enables security teams to pinpoint and extinguish your most critical risks.

Rapid7 Introduces Exposure Command to Eliminate the Security Visibility Gap

Security and IT teams are experiencing a significant (changed from “seismic” for clarity) shift in operations as they become more distributed. Development and procurement processes have decentralized, and sensitive data now extends far beyond the network edge. This expansion, coupled with growth and innovation outpacing security investments, has led to a significant “security visibility gap.”

Rapid7 Introduces Exposure Command to Eliminate the Security Visibility Gap

Disparate tools widen this gap, creating data silos and inconsistencies, leading to manual efforts and swivel-charing to manually correlate conflicting findings and dashboards. This situation has been exacerbated by broader industry trends. Gartner estimates that through 2026, ‘unpatchable’ attack surfaces will grow from less than 10% to more than half of the enterprise’s total exposure, reducing the effectiveness of traditional vulnerability management programs.

Security teams need to manage and interpret a broad range of different exposure types – cloud misconfigurations, user entitlements, unmanaged machines, vulnerabilities, etc. with conflicting and duplicate data from various different security and IT management tools with varying levels of data fidelity.

The only way to truly solve this problem is to implement a solution that treats third-party data as a first-class citizen, bringing together telemetry from all of your security tools to build a complete picture of your environment, and thereby your attack surface. To that end, Rapid7 announced the launch of two exciting new product offerings designed to unify your attack surface and deliver effective hybrid risk management: Surface Command and Exposure Command.

Unlock complete attack surface visibility to eliminate blind spots and uncover control gaps with Surface Command

Surface Command closes the visibility gap by breaking down data silos, combining internal and external monitoring to build a 360-degree view of your entire environment, combining market leading Cyber Asset Attack Surface Management (CAASM) and External Attack Surface Management (EASM) capabilities into one unified offering.

External scans provide an adversary’s perspective on the attack surface, detecting and validating exposures. Surface Command combines these external scans with a detailed inventory of your internal assets, continuously ingested and updated from a wide range of security and IT tools and automatically correlates the assets to create detailed inventory of your ‘true’ attack surface, highlighting security control gaps.

Rapid7 Introduces Exposure Command to Eliminate the Security Visibility Gap

This process delivers a comprehensive view of your environment that teams across the organization can trust and align on as a ‘single source of truth’ without the risk of blind spots, unprotected assets, and ungoverned access. Understanding how all your interconnected assets are configured enables you to quickly identify and prioritize  high-risk vulnerabilities, shadow IT, and compliance issues. With this more comprehensive visibility serving as the foundation of our Command Platform, security teams have a view of their attack surface they can trust and action across their wider organization.

Rapid7 Introduces Exposure Command to Eliminate the Security Visibility Gap

Automatically prioritize exposures across your hybrid environment with Exposure Command

Exposure Command extends the power of Surface Command even further, combining the same unified attack surface visibility with high-fidelity environment detail and risk context to help teams to zero-in on the exposures and vulnerabilities that attackers have in their sights with the threat-aware risk context needed to prioritize more efficiently and effectively.

With Exposure Command, every asset in your environment is enriched with relevant context from all of Rapid7’s exposure management capabilities, including our industry-leading VM, CNAPP and AppSec solutions, which provides teams an understanding of which assets are most critical to the business and those that suffer from toxic combinations that leave the organization vulnerable to a security incident.

This situational awareness allows teams to more effectively prioritize response efforts by honing in on the vulnerabilities that are either being actively exploited in the wild and/or those that present the most risk should a compromise occur.

Rapid7 Introduces Exposure Command to Eliminate the Security Visibility Gap

Prioritization is critical, especially when you consider the massive volume of risk signals produced by modern cloud-native environments on a daily basis. It’s simply not feasible to expect to address everything, so making sure that teams are spending the time they do have on the actions that will have the greatest impact on reducing their overall risk posture and eliminating critical exposures is key.

When it comes to prioritization, there are three primary vectors that we need to consider: Opportunity, Likelihood and Impact of exploitation.

  • Opportunity – The first step in prioritizing exposures is to understand whether a threat actor could exploit the issue in the first place by analyzing the downstream security controls and mechanisms in place – or not in place for that matter. This includes considering whether or not a resource is publicly accessible, if there are additional mitigating controls like web application or network firewalls, if an at-risk asset has an endpoint protection solution installed, etc.
  • Likelihood – It’s important to understand how likely it is that an attacker would exploit a given exposure. This can be accomplished in a number of ways, including focusing on CVEs on CISA’s Known Exploited Vulnerabilities (KEV) list, but also involves looking at real-world activity via threat intelligence feeds – like those that feed into Rapid7’s Active Risk score –  to get a sense for whether a vulnerability is being exploited elsewhere.
  • Impact – Taking into account the business criticality of the asset, data or system, what would be the relevant impact should a given risk signal be exploited by a threat actor. This is often accomplished by assigning tags that flag whether or not a given resource is associated with a business critical application or is housing sensitive customer data.

To this end, a new feature coming to the Command Platform with Exposure Command, Remediation Hub, automatically surfaces the top areas teams need to focus on and elevates the mitigation activities that would have the largest impact in reducing the overall risk score of your environment along with any relevant contextual information to assist in validation and remediation efforts.

Rapid7 Introduces Exposure Command to Eliminate the Security Visibility Gap

After 24+ years in exposure management, we are excited to partner with customers through the next era of the attack surface and hybrid risk with our new Exposure Command product. This is just the beginning. Stay tuned here for more updates as we continue to grow our Command Platform.

Learn more about Surface Command and Exposure Command

Attending Black Hat? Come see us at booth #2436 to get a one on one tour! If you can’t make it to the event you can also find additional information on the docs page, or give us a bit of information and we’ll have a member of the team reach out directly.

Celebrating Excellence: Rapid7 Recognized in Newsweek’s Greatest Workplaces in America 2024

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/07/31/celebrating-excellence-rapid7-recognized-in-newsweeks-greatest-workplaces-in-america-2024/

Celebrating Excellence: Rapid7 Recognized in Newsweek's Greatest Workplaces in America 2024

In a testament to its commitment to fostering an exceptional workplace environment, Rapid7 is proud to be included in Newsweek’s Greatest Workplaces in America for 2024. This recognition not only underscores Rapid7’s dedication to its people, but also cements its standing among companies that invest in employee satisfaction and well-being as a critical component of business success.

The Importance of Employee Engagement in the Workplace

Employee engagement in the workplace is linked to higher levels of productivity and positive business outcomes. According to Gallup’s State of the Global Workplace: 2023 Report, employees who are not engaged, or those who are actively disengaged, could cost the world $8.8 trillion in lost productivity.

Rapid7 understands this connection, and is intentional in providing a workplace where employees can do their best work while feeling valued and supported. Christina Luconi, Chief People Officer at the firm, states “As a business, we are relentlessly in pursuit of delivering the best possible outcomes for our customers and the cybersecurity community we are a part of. In order to do that, we need people who are prepared to challenge convention, offer constructive feedback, and work collaboratively to drive impact. We make sure this is possible by providing a work environment that offers flexibility, great teaming experiences, opportunities to grow and learn new skills, and a shared commitment to Rapid7’s mission and vision.”

America’s Greatest Workplaces: Award Criteria

More than 250,000 U.S. employees were interviewed for the ranking, resulting in over 1.5 million company reviews spanning 78 individual sectors. The survey covered topics such as compensation and benefits, training and career progression, work-life balance and company culture. Also, post-survey research considered each ranked company’s online mentions, diversity and inclusion ratings, and reviews of senior management.

How Rapid7 Supports Its Employees

Flexibility: Our default model is hybrid, with employees spending three days per week in the office. This flexibility aligns with our culture of collaboration and teamwork, and is designed to foster meaningful connections and trusting relationships.

Career Development: At Rapid7, we provide a platform for career development and growth. Through a combination of programs and hands-on experiences, employees have the ability to drive their career forward and own their development journey.

Collaboration: We encourage our people to seek out opportunities to learn about other teams and areas of the business. Collaboration is something that happens every day, whether we are gathering feedback and perspectives to get the best solution, or setting up an insight coffee to learn more about a person’s role. We encourage employees at all levels of the business to proactively find ways to partner, collaborate, and learn from one another.

Wellbeing and Benefits: Benefits vary by country, and in the United States, employees enjoy unlimited PTO, competitive paid leave options for new parents, mental health resources, access to financial advisers, and more. We also undergo an annual compensation analysis to ensure our pay practices are both competitive and equitable.

Looking Ahead

Being named one of Newsweek’s Greatest Workplaces in America for 2024 is a significant achievement for Rapid7. Our commitment to fostering a positive and inclusive work environment remains unwavering, and we look forward to continuing to evolve our programs as  we expand our teams and tackle new challenges in cybersecurity.

VMware ESXi CVE-2024-37085 Targeted in Ransomware Campaigns

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/07/30/vmware-esxi-cve-2024-37085-targeted-in-ransomware-campaigns/

VMware ESXi CVE-2024-37085 Targeted in Ransomware Campaigns

On Monday, July 29, Microsoft published an extensive threat intelligence blog on observed exploitation of CVE-2024-37085, an Active Directory integration authentication bypass vulnerability affecting Broadcom VMware ESXi hypervisors. The vulnerability, according to Redmond, was identified in zero-day attacks and has evidently been used by at least half a dozen ransomware operations to obtain full administrative permissions on domain-joined ESXi hypervisors (which, in turn, enables attackers to encrypt downstream file systems). CVE-2024-37085 was one of multiple issues fixed in a June 25 advisory from Broadcom; it appears to have been exploited as a zero-day vulnerability.

Per Broadcom’s advisory, successful exploitation of CVE-2024-37085 allows attackers “with sufficient Active Directory (AD) permissions to gain full access to an ESXi host that was previously configured to use AD for user management by re-creating the configured AD group (‘ESXi Admins’ by default) after it was deleted from Active Directory.”

Notably, Broadcom’s advisory differs from Microsoft’s description, which says: “VMware ESXi hypervisors joined to an Active Directory domain consider any member of a domain group named "ESX Admins" to have full administrative access by default. This group is not a built-in group in Active Directory and does not exist by default. ESXi hypervisors do not validate that such a group exists when the server is joined to a domain and still treats any members of a group with this name with full administrative access, even if the group did not originally exist.”

Also of note: While the VMware advisory indicates ESXi Admins is the default AD group, the Microsoft observations quoted in this blog all indicate use of ESX Admins rather than ESXi Admins.

ESXi hypervisors have been a popular target for ransomware groups in years past. Notably, since ESXi should not be internet-exposed, we would not expect CVE-2024-37085 to be an initial access vector — adversaries will typically need to have already obtained a foothold in target environments to be able to exploit the vulnerability to escalate privileges.

Exploitation

Microsoft researchers discovered CVE-2024-37085 after it was used as a post-compromise attack technique used by a number of ransomware operators, including Storm-0506, Storm-1175, Octo Tempest, and Manatee Tempest. The attacks Microsoft observed included use of the following commands, which first create a group named “ESX Admins” in the domain and then adds a user to that group:

net group “ESX Admins” /domain /add
net group “ESX Admins” username /domain /add

Microsoft identified three methods for exploiting CVE-2024-37085, including the in-the-wild technique described above:

  • Adding the “ESX Admins” group to the domain and adding a user to it (observed in the wild): If the “ESX Admins” group doesn’t exist, any domain user with the ability to create a group can escalate privileges to full administrative access to domain-joined ESXi hypervisors by creating such a group, and then adding themselves, or other users in their control, to the group.
  • Renaming any group in the domain to “ESX Admins” and adding a user to the group or using an existing group member: This requires an attacker to have access to a user that has the capability to rename arbitrary groups (i.e., by renaming one of them “ESX Admins”). The threat actor can then add a user, or leverage a user that already exists in the group, to escalate privileges to full administrative access.
  • ESXi hypervisor privileges refresh: Even if the network administrator assigns any other group in the domain to be the management group for the ESXi hypervisor, the full administrative privileges to members of the “ESX Admins” group are not immediately removed and threat actors still could abuse it.

Mitigation guidance

The following products and versions are vulnerable to CVE-2024-37085:

The Broadcom advisory on CVE-2024-37085 links to a workaround that modifies several advanced ESXi settings to be more secure; the workaround page notes that for all versions of ESXi (prior to ESXi 8.0 U3), “several ESXi advanced settings have default values that are not secure by default. The AD group "ESX Admins" is automatically given the VIM Admin role when an ESXi host is joined to an Active Directory domain.”

Broadcom VMware ESXi and Cloud Foundation customers should update to a supported fixed version as soon as possible. Administrators who are unable to update should implement workaround recommendations in the interim. ESXi servers should never be exposed to the public internet. Microsoft has additional recommendations on mitigating risk of exploitation in their blog.

Rapid7 customers

InsightVM and Nexpose customers who use ESXi hypervisors within their environments can assess their exposure to CVE-2024-37085 for the 8.x version stream with a vulnerability check available since June 2024. Support for scanning 7.0 is expected to be available in the July 30 content release.

InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on behavior related to this vulnerability:

  • Attacker Technique – Creation of "ESX Admins" Domain Group using Net.exe

From Top Dogs to Unified Pack

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/07/25/from-top-dogs-to-unified-pack/

Embracing a consolidated security ecosystem

From Top Dogs to Unified Pack

Cybersecurity is as unpredictable as it is rewarding. Each day often presents a new set of challenges and responsibilities, particularly as organizations accelerate digital transformation efforts. This means you and your cyber team may find yourselves navigating a complex landscape of multi-cloud environments and evolving compliance requirements.

So how does that translate into what cyber professionals have to deal with on a daily basis?

A Day in the Life of a Security Professional

In the Trenches

The responsibility of safeguarding sensitive data and protecting that very same data can create a constant pressure to stay one step ahead – of many things. Teams defending environments often face high stress levels and tight deadlines. Unsurprisingly, the demand for skilled security leaders often outpaces the supply of personnel. This is where an array of tools and solutions are introduced to support those teams. And while there are many positives to be had, security teams are often overrun by an array of solutions and vendors, creating increased complexity and vulnerabilities in their organization’s risk posture.

Multiple Vendors Often Means More Work

Using different vendors and solutions for various security functions can help keep things fresh, but it can also be time-consuming and cumbersome. And rather than help teams, it may lead to a decrease in performance. With each platform and tool requiring its own resources, the overall efficiency of your infrastructure and processes may suffer. These performance issues can impact critical business operations and hinder productivity. For instance, by the time you receive a threat alert, the attacker could already be hard at work.

Security analysts require a streamlined work environment that enables them to understand the root cause of alerts from any source with a single click. They shouldn’t have to waste time switching between multiple tools to investigate and remediate potential threats. And when belts start tightening and resources become scarce, managing multiple vendors with different payment cycles can become frustrating.

It pays to find ways to create a security ecosystem without sacrificing the efficacy of its components. By reducing the number of disparate cyber solutions, security professionals can optimize effectiveness and efficiency, subsequently enhancing security posture and reducing their risk profile.

What are the Benefits of a Unified Security Ecosystem?

Widening visibility into your entire IT environment strengthens threat detection capabilities, allowing security teams to minimize the impact of potential cyberattacks. In fact, 41% of organizations surveyed by Gartner say consolidating security solutions improved their risk posture. For some organizations still clinging to the status quo of best of breed solutions, consider the following consolidation benefits when trying to gain executive-buy-in.

1. Identify Systems and Applications at Risk

A robust vulnerability management program should be your first port of call to help identify any systems or applications potentially at risk. It provides your security team with critical insight into potential weaknesses in your IT infrastructure and overall network. Importantly, it will enable you to properly manage and patch vulnerabilities that pose risks to the network, protecting your organization from the possibility of a breach.

2. Safeguard an Evolving Landscape with Real-time Monitoring

Continuous scanning and testing of applications are vital components of a robust security strategy. Consolidating your security tech stack into a centralized ecosystem offers the ability to monitor your infrastructure in real-time and receive in-depth reports for better cross-team collaboration. Actionable insight gained will give you and your security team the autonomy you need to stay ahead of evolving risks and proactively address potential vulnerabilities.

3. Broaden Visibility and Contextual Understanding

Avoid leaving your security team with isolated alerts that require manual investigation and correlation. Integrating data from multiple sources, including endpoints, networks, cloud environments, and applications offers a comprehensive view and analysis of threats across different layers of the IT environment. This holistic approach allows for better correlation of data across various vectors, uncovering complex attack patterns that might otherwise go unnoticed. Consider broadening your context with threat intelligence, providing information about actor groups, typical targets, TTP’s, and more.

How Rapid7 Can Help: Managed Threat Complete

Managed Threat Complete offers a simplified security stack, fueling your D&R program to give you a 24x7x365 SOC, IR, XDR technology, SIEM, SOAR, threat intelligence, and unlimited VRM in a single service. This ensures your environment is monitored round-the-clock and end-to-end by an elite SOC that works transparently with your in-house team, helping to further expand your resources. Learn more.

4. Automate Threat Hunting and Distinguish Friend from Foe

In the face of ever-evolving threats, automating threat hunting becomes a crucial capability. By integrating automation within your consolidated security ecosystem, you’ll be able to quickly discern whether incoming threats are benign or malicious. Streamlined processes allow for efficient identification of potential risks, enabling you and your team to prioritize your efforts for activities that require human effort.

5. Prioritize Risk and Simplify Workflows

The sheer volume of security alerts can overwhelm even the most robust security operations. A consolidated security ecosystem mitigates this challenge by automatically grouping related alerts and prioritizing events that demand immediate attention. Unifying and visualizing activities in one place more rapidly identify the root causes of threats and their potential impact. Armed with this knowledge, you can assess the scope of an incident efficiently, build a timeline of the attack, and take swift, targeted action to effectively neutralize the threat.

6. Swiftly Investigate with End-to-end Digital Forensics

Incident resolution demands a thorough understanding of the attack’s entry point and the ability to track down any traces left by adversaries. With a consolidated security ecosystem, conduct swift and comprehensive investigations using end-to-end digital forensics and review key artifacts such as event logs, registry keys, and browser history across your entire IT environment — significantly enhancing your incident response capabilities. A full view of attacker activity can help you determine the extent of the compromise, identify weaknesses in your defences, and take appropriate remedial actions.

7. Coordinate Responses with Remediation and Policy Enforcement

Enable coordinated responses and future-proof defenses by integrating prevention technologies across your entire tech stack. Leverage communication between various security components and take decisive action against active threats in real-time. For example, an attack blocked on the network can automatically update policies on endpoints, ensuring consistent security measures across your infrastructure. This proactive approach to security ultimately reduces the risk of successful cyberattacks.

Consolidate to Mitigate

With a rapidly changing threat landscape, consolidation offers the security improvements your organization needs to give it the balance of power. Simplifying and streamlining your cybersecurity solutions begins with gaining visibility into your tech stack. This enables your team to identify where consolidation can improve your team’s productivity and effectiveness in detecting and mitigating risk.

Boston Business Journal Names Rapid7 as a Best Place to Work in Boston

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/07/09/rapid7-recognized-as-a-best-place-to-work-in-boston-by-the-boston-business-journal/

Boston Business Journal Names Rapid7 as a Best Place to Work in Boston

On June 13th, 2024, Rapid7 was recognized by The Boston Business Journal as a Best Place to Work in Boston. This marks the 13th consecutive year Rapid7 has made the list, this time coming in at #8 in the extra large company category. Best Places to Work rankings are based on anonymous employee surveys where workers rank how they feel about their employer. Questions range from employee engagement and impactful work, to career growth opportunities and having the support of their managers and leaders.

Christina Luconi, Chief People Officer at Rapid7, credits the recognition to the company’s ability to attract, develop, and support exceptionally talented team members across all areas of the business.

“When you are able to get a group of talented people aligned to a shared vision and mission, and you invest in resources to support them in learning and growing their careers, you’re able to create the foundation for both a successful business, and an incredible workplace that people are really proud of,” she said.

Boston is home to Rapid7’s global headquarters, which sits at 120 Causeway Street adjacent to TD Garden and North Station. The location was chosen due to a variety of factors, including easy access to public transportation for employees. The company operates on a hybrid model with employees spending 3 days a week in the office and 2 days working remotely. Inside, employees have access to a variety of working spaces and zones. Designated quiet areas and private meeting rooms equipped with Zoom technology and whiteboards support more focused or heads-down work, while community spaces like their Barista Bar, speakeasy, and living room seating areas foster collaboration and cross-functional interactions.

Rapid7’s Boston site is occupied by all business functions, including engineering, sales, people strategy, marketing, and finance.

To learn more about working at Rapid7, click here.