All posts by Rapid7

Built In Honors Rapid7 with “2025 Best Places To Work” Award

Post Syndicated from Rapid7 original https://blog.rapid7.com/2025/01/09/built-in-honors-rapid7-with-2025-best-places-to-work-award/

3 Rapid7 Offices Included in Built In’s “Best Places to Work” Lists

Built In Honors Rapid7 with “2025 Best Places To Work” Award

Built In has announced that Rapid7 is being honored in the 2025 Best Places To Work Awards. Specifically, Rapid7 earned recognition for three office locations: Austin, Boston, and Arlington (Washington DC). The annual awards program includes companies of all sizes, from startups to those in the enterprise, and honors both remote-first employers as well as companies in large tech markets across the U.S.

“When employees join Rapid7, they quickly see how much we care for our people and their experience with us. Through competitive compensation packages, inclusive benefits, and a variety of location specific perks and amenities, we’re committed to ensuring our people are supported in doing their most impactful and creative work.” says Christina Luconi, Chief People Officer at Rapid7.

Lists where Rapid7 offices were featured include:

  • 100 Best Large Places to Work Austin
  • 100 Best Large Places to Work Boston
  • 100 Best Large Places to Work Washington DC (for our Arlington office)
  • 100 Best Places to Work (all sizes) Washington DC (for our Arlington office)

Built In determines the winners of Best Places to Work using company data about compensation and benefits. To reflect the benefits candidates are searching for more frequently on Built In, the program also weighs criteria like remote and flexible work opportunities, programs for DEI and other people-first cultural offerings.  

“Being recognized as a Best Place to Work is a testament to these companies’ commitment to building a workplace where individuals and innovation thrive,” says Built In CEO and Founder, Maria Christopoulos Katris. “At Built In, we understand that great companies are powered by great teams, and this achievement showcases their dedication to fostering a culture of growth, inclusivity, and excellence. Congratulations on this well-deserved honor.”

Rapid7 believes that when it comes to creating an exceptional workplace, winning an award doesn’t mean the job is done. Our Workplace Experience and People Strategy teams embrace our core value of ‘Never Done’ by evaluating and evolving our offerings, so our people can build the career experience of a lifetime. Awards like these are one of many components we leverage to ensure we are on the right track, and we look forward to the continued evolution of our workplaces in 2025 and beyond.

Want to learn more about working at Rapid7? Click here for our careers site.

Rapid7 Recognized with Top Score of 100 in 2025 Corporate Equality Index

Post Syndicated from Rapid7 original https://blog.rapid7.com/2025/01/07/rapid7-recognized-with-top-score-of-100-in-2025-corporate-equality-index/

Rapid7 Recognized with Top Score of 100 in 2025 Corporate Equality Index

On January 7, the Human Rights Campaign Foundation released their 2025 Corporate Equality Index (CEI), where Rapid7 earned a top score of 100.

The CEI is the nation’s leading benchmark for LGBTQ+ workforce equality, evaluating policies and practices in areas such as non-discrimination, equitable benefits, inclusive cultures, and corporate social responsibility. With this score, Rapid7 is recognized as a leader in LGBTQ+ Workplace Inclusion.

This recognition reflects Rapid7’s core value; and our commitment to creating a dynamic workplace where all people can build a rewarding career. Our core value  ‘Bring You’ is an invitation for everyone to embrace their uniqueness and bring their true selves to the workplace. We know that fostering a culture of inclusion enables people to be more creative and generate innovative ideas – essential skills when working in the field of cybersecurity. Additionally, we recognize that our work in this space is truly ‘Never Done’. We continuously evaluate, optimize, and seek feedback on programs and practices that support diversity, equity, and inclusion across the business. We’re proud of this recognition, and will continue to work towards building and maintaining a workplace where all people have access to the tools, resources, and communities that enable them to feel seen and valued, so they can make an incredible impact through their work.

In consideration for this recognition, the CEI examined Rapid7’s practices and policies against four core pillars:

• Non-discrimination policies across business entities

• Equitable benefits for LGBTQ+ workers and their families

• Supporting an inclusive culture; and,

• Corporate social responsibility

“HRC Equality Index recognition reflects a gold standard, one that ensures employees—regardless of their lived experience—have equitable access to benefits and are treated inclusively. We alignwith the HRC Equality Index standard, as we believe it fosters an environment that enables employees to bring their authentic selves to work. By cultivating an environment that nutures this dynamic, we empower our people to perform at their best and contribute meaningfully to the success of our business.

Additionally, achieving recognition on the HRC Equality Index underscores our broader commitment to being an employer who strives to reflect the global community we seek to secure. This milestone also highlights how essential equity is to our mission. Equity is a key part of the equation, and it is vital that we never lose sight of its importance.

I am incredibly proud that we are included on the index this year. This achievement reflects our ongoing commitment to fostering innovation, belonging, and excellence in all that we do.”

In addition to offering equitable benefits, Rapid7’s employee resource groups provide opportunities for people to come together around shared experiences. The Pride community provides space for LGBTQ+ employees and their allies to raise visibility and provide support through various virtual and in-office events. These initiatives include hosting external speakers, facilitating open discussions, and organizing celebrations.

To learn more about Rapid7 as a workplace, visit our careers page today.

Navigating Choppy Waters: Top Security Predictions from Rapid7’s 2025 Webinar

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/12/12/navigating-choppy-waters-top-security-predictions-from-rapid7s-2025-webinar/

Navigating Choppy Waters: Top Security Predictions from Rapid7's 2025 Webinar

It’s that time of year again — one year is ending and another is set to begin.. And what a year it’s been for the security community! The sheer scale of incidents has left SecOps teams breathless, so thinking about what could be in store next year can be overwhelming.

But there’s no need to panic; despite the disruption, the community has rallied together and risen to the challenge, demonstrating adaptability, collaboration, and resilience. And, most of all, why this industry isn’t for the faint of heart!

Over the last few years, we’ve seen significant interest in our annual Security Predictions webinar. Security teams use the session to take stock of the current year and use the predictions to get a head start on planning for the next.

This year, the webinar was shot in person from Rapid7’s office in Belfast, a city that has emerged as a modern tech innovation hub. From its origins as the shipyards that birthed the Titanic, Belfast’s history is a testament to both ambition and resilience, so it is fitting that this city served as the stage for Rapid7’s annual Security Predictions webinar.

Hosted by industry heavy hitter Brian Honan, CEO of BH Consulting, the webinar brought together Rapid7 security and policy experts Raj Samani, Chief Scientist, and Sabeen Malik, VP of Global Government Affairs and Public Policy.

Looking Back: 2024’s Predictions in Review

Before diving into the future, the panel revisited their predictions for 2024, which focused on three core areas:

1. Increasing risks and regulations will intensify pressure on businesses to navigate evolving demands across a complex global landscape.

Sabeen Malik highlighted that the forecasted rise in cyber regulations materialized, with frameworks like NIS2 and the SEC’s cybersecurity mandates intensifying global compliance demands.

2. Expect a surge in the growth of real-time information sharing within global public-private cyber partnerships.

While strides were made, Raj Samani noted that much of the shared data lacks actionable context, calling for enriched, actionable intelligence that organizations can immediately act upon.

3. The continued use of zero-day vulnerabilities exploited by ransomware groups will compel SOCs to focus on exposure management and validation strategies.

As predicted, ransomware groups continued to exploit zero-day vulnerabilities, a trend exacerbated by their increasing sophistication and access to novel attack vectors.

“2024 was pretty much on the button,” said Brian Honan. “The predictions were accurate, but the challenges they highlighted are far from over.”

2025 could be Iceberg Alley/Visibility as a Life Preserver

Prediction 1: Greater visibility will act as a life preserver for security teams treading water across an increasingly complex attack surface.

Visibility isn’t just a cybersecurity buzzword—it’s the foundation of effective defense. Raj Samani summarized this challenge succinctly: “You can’t protect what you don’t know about.”

In today’s environment, where assets span on-premise systems, cloud services, and third-party integrations, organizations often need help to map their full attack surface. Raj explained how conflicting data from multiple tools complicates this task: “Your endpoint provider says one thing, your VPN provider says another — how do you normalize this information?”

After further discussion, the panellists provided a short, medium and long-term action plan to help defenders strengthen their visibility.

Prediction 2: To thrive in a world where regulatory change is an ongoing concern, SecOps should prepare for both the predictable and the unpredictable.

In cybersecurity, the only constant is change. The panel emphasized the need for agile Security Operations Centers (SOCs) to respond effectively to both expected and unexpected threats.

“This is about moving beyond checkbox exercises,” said Sabeen. “SOC teams must adopt continuous processes and infrastructure to manage a rapidly changing landscape.” She pointed to regulatory frameworks like DORA and NIS2, which mandate real-time monitoring and frequent vulnerability assessments, as drivers of this shift.

The panelists also provided an action plan that prioritizes incident response, real-time threat detection, and continuous vulnerability management to meet evolving compliance and security needs.

Prediction 3: Cybercriminals will increasingly exploit zero-day vulnerabilities, expanding potential entry points and bypassing traditional security measures to deliver more ransomware attacks.

Ransomware remains a dominant threat, evolving as attackers adopt zero-day vulnerabilities to bypass traditional defenses. Raj explained how this shift is lowering the technical barriers for cybercriminals: “Access to zero-days allows even unsophisticated actors to execute devastating attacks.”

The professionalization of ransomware groups further exacerbates the threat. As Sabeen noted, “This is no longer a scattered effort. It’s a highly organized, professional ecosystem, and it’s growing at an unsustainable rate.”

The team outlined an action plan to combat ransomware, including the critical action step of engaging organizational leadership to prioritize cybersecurity investments and ensure board-level awareness of the risks.

“Use this as an opportunity to have meaningful discussions with your board,” Raj advised. “Ransomware is a top concern, and preparation is key.”

Final Thoughts: Staying Resilient in Choppy Waters

While the challenges of 2025 may seem daunting, the panel concluded on a hopeful note. Raj highlighted Rapid7’s commitment to empowering the industry through open-source tools and resources like AttackerKB, Metasploit, and Velociraptor.

“Don’t be overwhelmed,” Raj said. “We’re all in this together, and Rapid7 is here to help with actionable insights and tools that protect what matters most.”

As Brian wrapped up, he reflected on Belfast’s legacy and the lessons it offers. “The Titanic reminds us of both the heights of ambition and the importance of preparation. In cybersecurity, as in life, visibility, adaptability, and resilience are the keys to navigating choppy waters.”

To get a full understanding of what 2025 could bring, watch the Top Cybersecurity Predictions webinar on-demand.
Widespread exploitation of Cleo file transfer software (CVE-2024-50623)

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/12/10/etr-widespread-exploitation-of-cleo-file-transfer-software-cve-2024-50623/

Widespread exploitation of Cleo file transfer software (CVE-2024-50623)

On Monday, December 9, multiple security firms began privately circulating reports of in-the-wild exploitation targeting Cleo file transfer software. Late the evening of December 9, security firm Huntress published a blog on active exploitation of three different Cleo products (docs):

  • Cleo VLTrader, a server-side solution for “mid-enterprise organizations”
  • Cleo Harmony, which provides file transfer capabilities for “large enterprises”
  • Cleo LexiCom, a desktop-based client for communication with major trading networks  

Huntress’s blog says the exploitation they’re seeing across Cleo products results from an insufficient patch for CVE-2024-50623, a vulnerability disclosed in Cleo VLTrader, Cleo Harmony, and Cleo LexiCom in October 2024. Cleo indicated that the vulnerability was fixed in version 5.8.0.21 of all three solutions, but according to Huntress, 5.8.0.21 remains vulnerable to exploitation. CVE-2024-50623 is a cross-site scripting issue (CWE-79) that allows for unauthenticated remote code execution on target systems.

Update: Cleo evidently communicated with customers on December 10 acknowledging a “critical vulnerability in Cleo Harmony, VLTrader, and LexiCom that could allow an unauthenticated user to import and execute arbitrary bash or PowerShell commands on the host system by leveraging the default settings of the Autorun directory.”

As of December 10, Rapid7 MDR has confirmed successful exploitation of this issue in customer environments; similar to Huntress, our team has observed enumeration and post-exploitation activity and is investigating multiple incidents.

File transfer software continues to be a target for adversaries, and for financially motivated threat actors in particular. Rapid7 recommends taking emergency action to mitigate risk related to this threat.

Mitigation guidance

The following products and versions are vulnerable to CVE-2024-50623. The information below contradicts previous vendor guidance, which indicated that 5.8.0.21 resolved the issue. Cleo has updated their advisory as of December 10, 2024 to confirm 5.8.0.21 is still vulnerable.

  • Cleo Harmony before and including version 5.8.0.21
  • Cleo VLTrader before and including version 5.8.0.21
  • Cleo LexiCom before and including version 5.8.0.21

According to Huntress, “Cleo is preparing a new CVE designation and expects a new patch to be released mid-week.”

In the absence of an effective patch for CVE-2024-50623 (and any other CVEs that may be assigned to this exploit), Cleo customers should remove affected products from the public internet, ensuring they are behind a firewall. Per Huntress’s investigation, disabling Cleo’s Autorun Directory, which allows command files to be automatically processed, may also prevent the latter part of the attack chain from being executed.

Huntress’s blog has several descriptions of post-exploitation activity, including attack chain artifacts, commands run, and files dropped for persistence. Rapid7 recommends that affected customers review these indicators and investigate their environments for suspicious activity dating back to at least December 3, 2024.

Rapid7 customers

InsightVM and Nexpose customers will be able to assess their exposure to CVE-2024-50623 on Windows with an authenticated vulnerability check expected to be available in today’s (Tuesday, December 10) content release. Please note that content releases are typically available late in the evening ET on Patch Tuesday.

InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of rules deployed and alerting on behavior related to this threat:

  • Suspicious Process – XORed Data in PowerShell
  • Suspicious Process – PowerShell System.Net.Sockets.TcpClient
  • Attacker Behavior – Possible Cleo MFT Exploitation 2024
  • Attacker Tool – PowerShell -noni -ep -nop Flags
  • Attacker Behavior – Obfuscated Powershell Script Containing -noni -ep -nop Flags
  • Suspicious Process – Powershell Invoke-WebRequest

Expanded SOC Coverage Into AWS Environments with Rapid7 MXDR

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/12/03/expanded-soc-coverage-into-aws-environments-with-rapid7-mxdr/

Co-athored by Mikayla Wyman and Ryan Blanchard

Expanded SOC Coverage Into AWS Environments with Rapid7 MXDR

As organizations increasingly rely on AWS for scalability and innovation, the complexity of securing these environments grows. AWS offers a robust set of native services and a comprehensive ecosystem, but managing security signals and responding to threats across dynamic workloads can overwhelm even the most well-equipped teams.

Rapid7’s Managed Extended Detection and Response (MXDR) service has focused on helping customers bridge this gap, unifying security telemetry from major cloud service providers including AWS and Azure, with expert-driven detection and response. With MXDR, organizations can confidently scale their cloud investments without sacrificing the comprehensive coverage they’re familiar with today.

Tailored to AWS Workloads and Modern Cloud Security Challenges

MXDR delivers the context and coverage needed to handle complex threats in AWS environments, providing a purpose-built service to address the specific challenges of securing modern cloud environments. With the extension of MXDR for AWS, teams can tailor their Rapid7 MXDR support to include triage, investigation, and response for critical GuardDuty alerts directly within their MDR service.

Layering native AWS telemetry with insights from other tools and environments creates a centralized, unified view of your security posture. With this context, our team is able to tailor protections and actions to the unique needs of your environment, safeguarding your assets more effectively against evolving threats. This comprehensive perspective empowers Rapid7 MDR analysts to operate at peak efficiency, ensuring your organization experiences a robust incident response lifecycle, from initial detection and alert triage to containment and response.

Augmenting Your Security Team with a Fleet of CDR Experts

Protecting your AWS environment doesn’t need to be a solo effort. With Rapid7 MXDR, you gain access to our extensive team of seasoned MDR analysts who diligently monitor, triage, and respond to incidents in real time, reducing operational burden. With an expert MDR team on call, teams are ready to contain incidents and limit blast radius. Customized mitigation and response strategies for AWS workloads, aligned with your unique environment and risk tolerance enables our team to provide clear insights, remediation guidance and future mitigation recommendations to improve security and drive executive buy-in for security investments.

By deeply integrating cloud risk context from our industry-leading CNAPP capabilities into the incident response workflow, our MDR analysts are equipped with environmental awareness needed to act more quickly on your behalf to stop attackers in their tracks.

Rapid7 MXDR eliminates the need for piecemeal tools and processes by delivering end-to-end security services that combine AWS-native telemetry with cross-platform intelligence. The result is comprehensive threat detection and mitigation across your AWS environments without the complexity of managing multiple tools, providing:

  • Cloud Attack Surface Visibility and Advanced Threat Detection: Correlating AWS telemetry with global threat intelligence to build a dynamic map of your environment, uncover sophisticated attacks and spot avenues for lateral movement.
  • Continuous Coverage and Proactive Threat Hunting: Lean on our team of seasoned SOC experts who monitor, triage, and respond to incidents in real time, reducing operational burden.
  • Visibility into Cloud Identities, Their Permissions and Privileges: Monitor all cloud accounts and identities and proactively spot anomalous and potentially malicious user behavior, privilege escalations, or unusual API calls.
  • AI-Assisted Triage with Risk-Aware Context: Automatic context enrichment for cloud alerts with the relevant information SOC analysts need to understand the posture of a compromised account or resource and prioritize response.

Take Command of Your AWS Security Today

Whether you’re protecting critical workloads or responding to active threats, Rapid7 MXDR enables organizations to secure their AWS environments with confidence. From continuous monitoring to expert response, Rapid7 ensures your AWS assets remain protected while allowing your team to focus on driving business innovation.

Contact Rapid7 today to see how MXDR can elevate your AWS security posture.

Rapid7 Recognized for ‘Excellence in Workplace Health and Wellbeing’ at the Belfast Telegraph IT Awards

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/11/19/rapid7-recognized-for-excellence-in-workplace-health-and-wellbeing-at-the-belfast-telegraph-it-awards/

Rapid7 Recognized for ‘Excellence in Workplace Health and Wellbeing’ at the Belfast Telegraph IT Awards

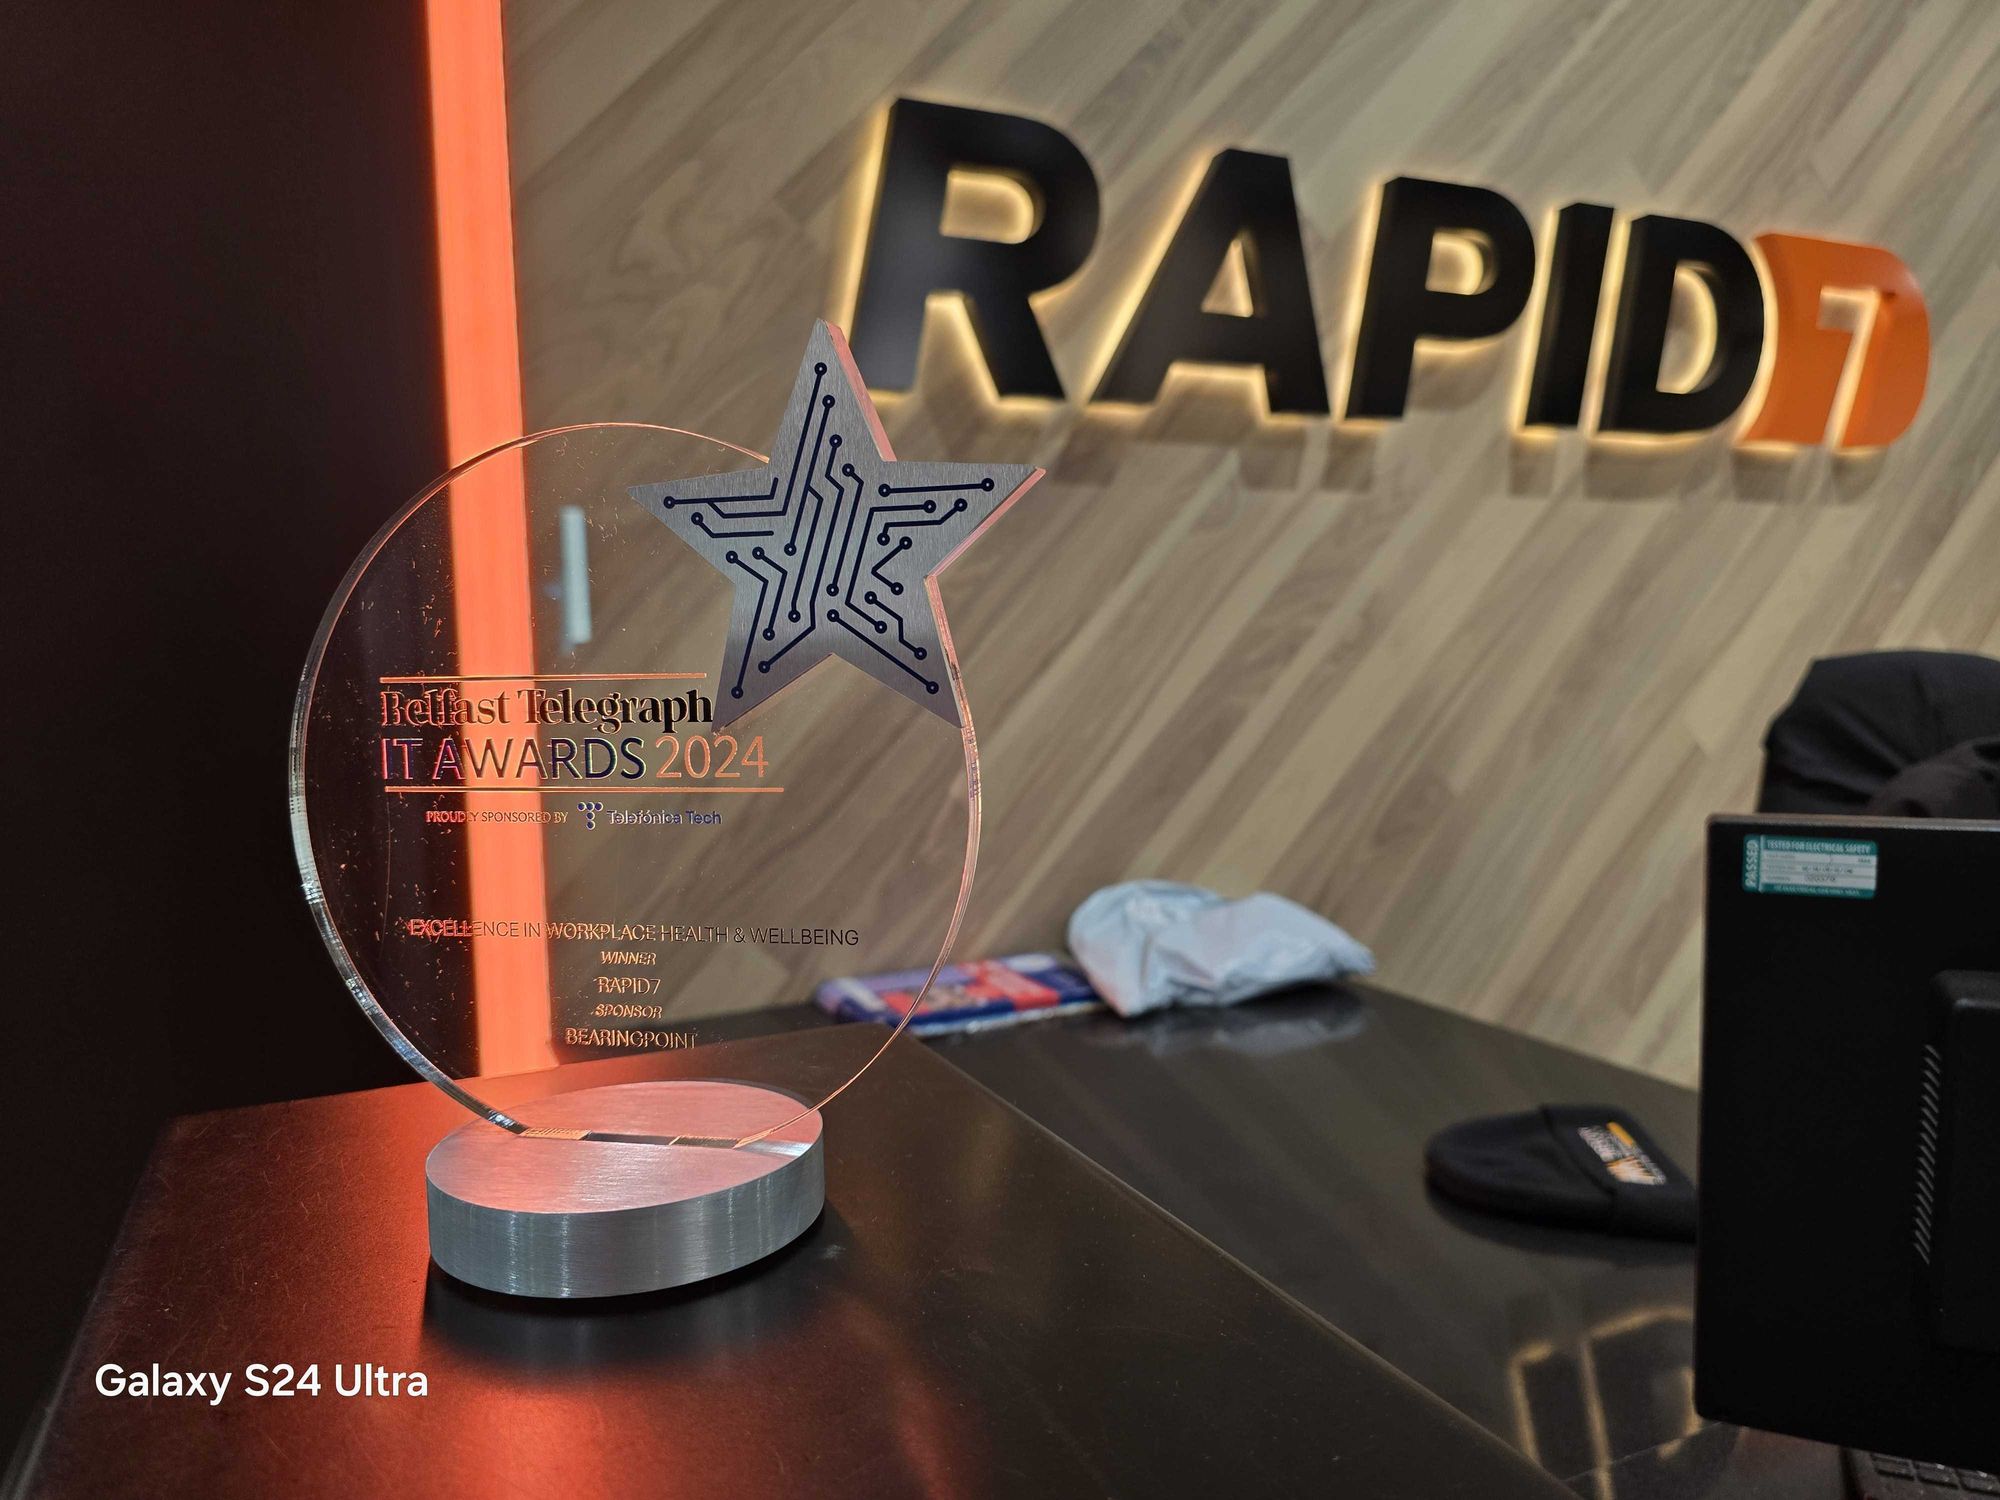
On Friday, November 15th, Rapid7 was awarded ‘Excellence in Workplace Health and Wellbeing’ at the Belfast Telegraph IT Awards. This award recognizes technology companies in Belfast that prioritize employee well-being.

At Rapid7, we believe that the best ideas and solutions come from diverse, multi-faceted teams. By supporting our people with programs that enhance their well-being and quality of life, we create an environment where they can continue to have rewarding career experiences and make an incredible impact on our business. Our programs go beyond just taking care of people when they are sick. Instead, we look to increase their overall quality of life with unique initiatives and offerings that support both physical and mental health and wellness.

Our award submission was broken down into three key areas where we offer unique benefits that make us leaders in our field. These areas included benefit offerings, physical health and well-being, and mental health and well-being.

Benefit Offerings

Rapid7 is proud to offer unique and competitive benefits to employees and their families. One example is our neurodiversity coverage. Employees at Rapid7, and their family members, have access to specialists for evaluations, screenings, and treatment programs. Appointments and services that would otherwise take months or years are able to happen within weeks.

As part of our health benefit program, once a year, our company participates in a global health and well-being challenge. This is not your typical ‘steps’ challenge, but instead a comprehensive initiative encompassing physical activity, meditation, and mindfulness, designed to build connections across Rapid7 teams.

Physical health and well-being

Our cycle-to-work scheme allows employees to set aside a salary sacrifice to purchase a new bicycle. There is no maximum limit so our employees are often able to select high-end models at an affordable rate. Employees drop in and out of the program as they wish, and this year we have 16 employees saving up to get their new bikes.

For those who prefer a gym or fitness classes, our Chichester street office building is equipped with a full service gym featuring cardio and weight training equipment, as well as a yoga and group fitness studio. The fitness studio has a variety of virtual program on demand, many of which can be completed in just 20 minutes, making it easy for employees to fit in a quick break during their day.

Mental health and wellbeing

AwareNI is a local organization that we’ve been proud to partner with. We participate in their mood matters program, bringing mental health awareness and training to employees across Rapid7. However, what is most unique is our on-site mental health first aiders. We partner with AwareNI to train employees to be on-site mental health first aiders, giving employees a resource in the office to go to if they are experiencing a mental health crisis. As mental health first aiders, these employees are equipped with the skills and knowledge to guide and support colleagues experiencing a mental health-related crisis.

At Rapid7, we are on a mission to create a secure digital world for our customers, our industry, and our communities. We show up every day to keep our 11,000+ customers around the world protected from the latest threats. This requires us to build a dynamic workplace where innovation and collaboration thrive. Taking care of our people is a critical first step, and we’re honored to have been recognized as a leader in this space. To learn more, please visit our careers site at careers.rapid7.com.

New IDR Log Search Enhancements: Accelerate, Streamline, and Simplify Investigations

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/11/15/new-idr-log-search-enhancements-accelerate-streamline-and-simplify-investigations/

Co-authored by Ed Montgomery & René Fusco, Rapid7

New IDR Log Search Enhancements: Accelerate, Streamline, and Simplify Investigations

In today’s cybersecurity landscape, organizations need robust detection and response solutions to stay ahead of evolving threats. Rapid7’s InsightIDR, the foundation of our Managed Detection and Response (MDR) service, empowers security teams with advanced analytics, automation, and expert-led investigations. Whether used as a standalone SIEM and XDR platform or in combination with MDR, InsightIDR’s latest Log Search enhancements bring even more value  across the board. These updates accelerate response times, simplify complex queries, and improve the investigation process for both our MDR clients and product-only customers.

These updates, including Simplified Query Building, Pre-Computed Queries, and Bloom Filters, enhance the speed, accuracy, and accessibility of log search for security teams, ensuring faster, more targeted threat investigations for organizations.

Let’s explore how these updates elevate the detection and response lifecycle.

Simplified Query Building: Empowering Analysts to Act Faster

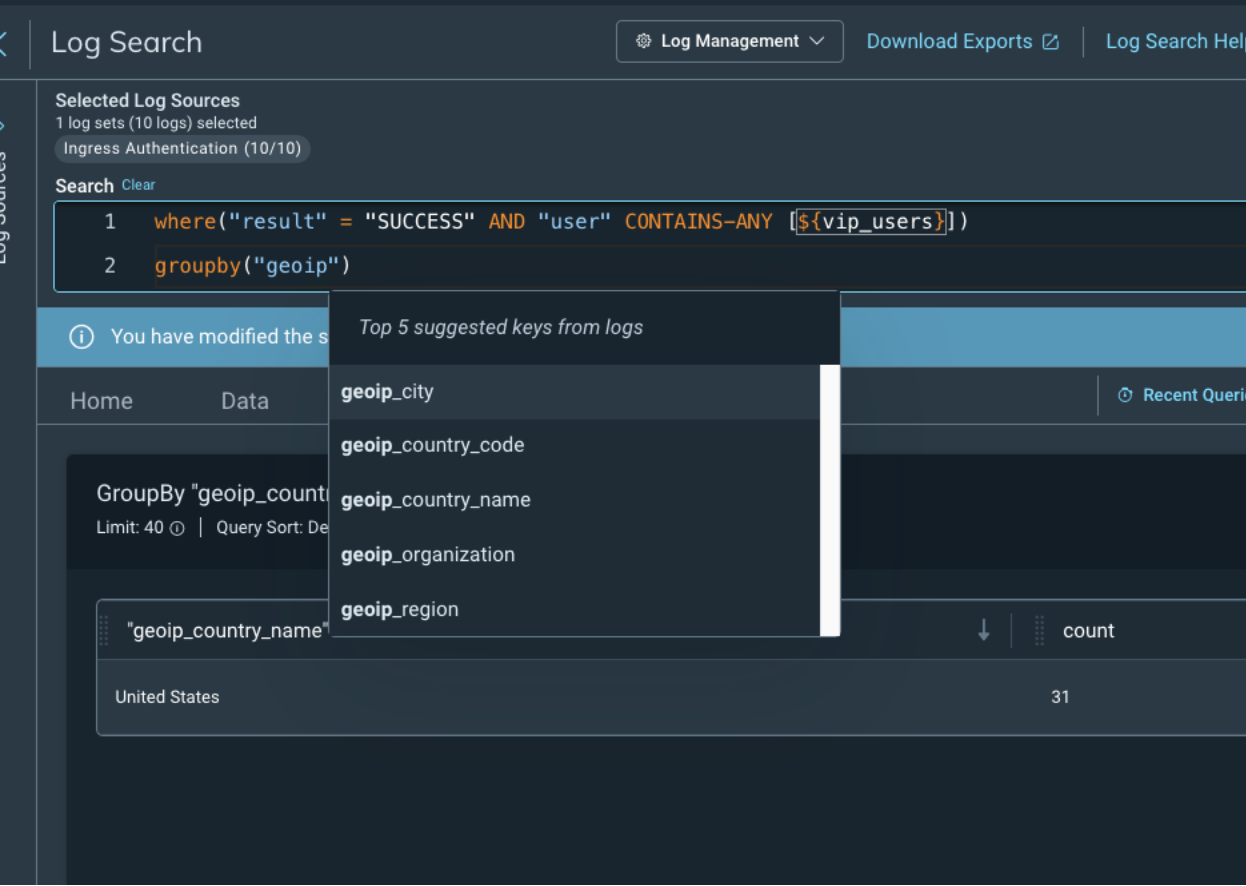
A key element of any detection and response solution is the ability to quickly turn data into actionable insights. Simplified Query Building enables analysts to construct and refine log searches faster, without complex syntax or technical details. This user-friendly interface enables any InsightIDR user, regardless of technical expertise, to create advanced queries through point-and-click prompts, accessing critical data quickly to streamline investigations.

By lowering the barrier to creating queries, Simplified Query Building provides organizations with timely, data-backed insights into incidents, reducing investigation time for both Rapid7’s MDR team and InsightIDR customers. This update ensures that every security team member, regardless of tenure, can access and leverage the power of InsightIDR’s log data without becoming bogged down by technical complexities.

New IDR Log Search Enhancements: Accelerate, Streamline, and Simplify Investigations
InsightIDR – Simplified Query Building

Pre-Computed Queries: Reducing Time-to-Response for All Investigations

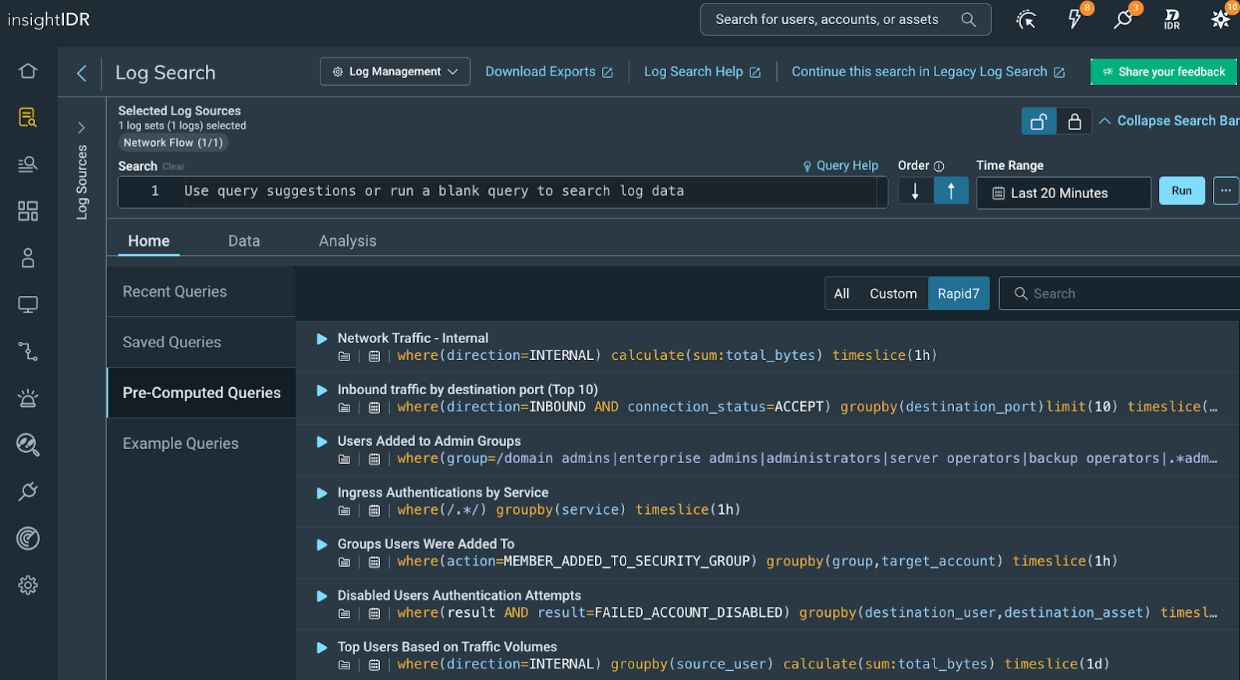
Time is critical when it comes to threat response.With Pre-Computed Queries (PCQs), both MDR and product-only customers benefit from reduced log search times. PCQs enable predictably fast, near-instant access to insights by pre-calculating query results in real-time as data arrives, enhancing responsiveness for all InsightIDR users.

Customer Feedback

“As an MSSP, InsightIDR’s ability to handle large amounts of data is key for identifying threats in our client environments. Pre-Computed Queries have reduced return times for complex searches by over 70%, allowing us to create more impactful insights for our clients.”

— Mat Cornish, Technical Director, Longwall Security

While InsightIDR already supports saving queries for reuse, PCQs take it further by pre-computing results, helping analysts to instantly identify patterns or gather evidence. Additionally, the Log Search home tab organizes queries by “Recent,” “Saved,” and “Pre-computed,” enabling users to quickly find what they need for streamlined incident handling. Whether you’re a customer conducting an in-house investigation or part of Rapid7’s MDR team, PCQs ensure faster insights and more efficient incident response.

New IDR Log Search Enhancements: Accelerate, Streamline, and Simplify Investigations
InsightIDR – Pre-Computed Queries

Bloom Filters: Accelerating Key Value Pair Searches for Precise Threat Hunts

Not all queries can be pre-calculated in advance. Security teams are frequently asked questions about potential exposure to specific indicators of compromise (IoCs), such as flagged IP addresses or hash values. With Bloom Filters, both MDR and product-only customers gain a performance boost in search time for precise threat hunts by reducing unnecessary data processing.

For exact match searches, like identifying a compromised IP address or hunting for a suspicious hash value where(hash.sha=”…”), Bloom Filters optimize search time by ruling out irrelevant data – enabling the algorithm to skip logs that would not have matches. This enhancement is implemented on the backend and occurs automatically for any search that contains an exact match key-value pair. Reducing the search space means accelerating analysts’ ability to hone in on the exact information they need, cutting down investigation time dramatically.

A recent research effort into InsightIDR’s new indexing approach, which leverages Bloom Filters, showed impressive results with:

  • Improved Efficiency: Approximately 40-60% of all searches have experienced noticeable speed improvements since deployment.
  • Increased Precision: The new index has enabled applicable queries to skip irrelevant data three to four times more effectively, leading to shorter search durations for even more efficient investigations.

Bringing It All Together: Faster, More Effective Detection and Response

Whether you’re a Rapid7 MDR customer or an InsightIDR product-only user, these Log Search updates significantly enhance detection and response capabilities. By reducing search times, simplifying complex queries, and pinpointing threats with greater accuracy, we provide every InsightIDR user with faster, more effective security outcomes.

This means:

  • Faster Detection: Pre-Computed Queries and Bloom Filters accelerate search processes, enabling quicker response to incidents across both MDR and product-only use cases.
  • Improved Visibility: Simplified Query Building ensures analysts can quickly refine searches and access the data needed for comprehensive investigations.
  • Targeted Threat Hunts: Optimized key-value pair searches focus on the most relevant data, delivering quicker results for security teams.

Want to see these improvements in action? Contact us today to learn how Rapid7’s MDR service can protect your organization. You can also try InsightIDR for free with a 30-day trial.

Cathal O’Neill – Taking Command of Your Career in Tech

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/11/07/cathal-oneill-taking-command-of-your-career-in-tech/

Cathal O’Neill - Taking Command of Your Career in Tech

Cathal O’Neill joined Rapid7 in 2023 as a Senior Engineering Manager, and he has since advanced to the role of Engineering Director. Reflecting on his career path, he says,“My journey into senior management has been a continual evolution, driven by both personal development and the desire to lead challenging technical projects.”

Cathal credits the experiences for paving a path of continuous growth and development. Beginning his career as an intern and moving through roles from engineer to team leader, he notes, “Through each role, I’ve gained deeper insights into the technical, managerial, and strategic aspects of technology leadership. As I navigated these roles, only then did I understand the scale at which software solutions need to operate and evolve.”

We asked what his key to success was, and he shared what he sees as three critical ingredients for taking command of your career in tech:

  • Feedback
  • Connections
  • Continuous Learning

Below, Cathal delves into each principle and offers resources and practical tips that have helped him along the way.

Feedback

“I often hear that feedback is a gift. This is something I know to be true today, but it took me a while to realise what this really meant, and get comfortable with it. Early in my career, I would get constructive feedback and feel defensive or try to prove that it wasn’t true. Once I started to embrace feedback and use it as an opportunity to learn, I was able to navigate challenges much more efficiently, and become a better leader for my team. Looking back, every major milestone in my career was shaped by feedback from team mates, managers and mentors.”

“Feedback is most effective when built on mutual trust. Early on, a mentor recommended Radical Candor, a book by Kim Scott that emphasises the importance of relationships in delivering constructive feedback. I’ve applied its principles to give and receive feedback in ways that feel authentic and lead to productive outcomes. The Software Engineering Guidebook by Gergely Orosz is another one that I have recently been reading, and using to frame my feedback and guidance to my teams. Orosz dives into both the technical aspects of the software roles, as well as providing advice on how to work within an organisation.”

Recommendation:

Connections

“As I navigate different situations, I’ve found myself very lucky to have a number of strong people around me who lean in to help me succeed. Whether it’s offering advice, critical or positive feedback, or “rubber ducking” with me (which I’ve found not just to be useful when debugging code!), these connections continue to shape my development today.

When building your network, I recommend:

  • Being intentional: Aim to build relationships with people whose experiences and career paths you value, as opposed to trying to grow your network for the sake of it.
  • Engaging thoughtfully: Do the groundwork to understand someone’s background and ask specific, meaningful questions. Genuine curiosity often forms the foundation of strong professional relationships.
  • Following up: Maintaining relationships requires effort. A quick message to check in, a note on how their advice helped, or a casual coffee catch-up can strengthen these connections over time.”

Continuous Learning

“Learning happens in many forms—through formal programs or hands-on experiences—and is something we feel very passionately about at Rapid7, as it relates to our core value of ‘Never Done.’ Shortly after joining, I participated in the Manager Bootcamp, which laid the foundation for understanding Rapid7’s leadership expectations. Later, I joined the Amplify program, which provides 360-degree reviews and insights from senior leaders, including our CEO, Corey Thomas. As I went through the Amplify programme, I read ‘Scaling people: tactics for management and company building, by Claire Hughes Johnson. This book helped reinforce concepts I was learning and is one that I would recommend to anyone in a leadership role.

Outside of these formal programmes, learning is embedded into our everyday culture and how we operate as a global company. In the Cloud Security engineering teams, we have lunch and learn sessions, show and tells, and have recently launched cloud technology and cloud security training, which cover the various cloud providers and industry certifications. At Rapid7, we are open to giving people stretch assignments or leaning in on new projects that relate to an area or topic they are interested in and want to learn more about. If you want to do something different or specialise in another area of the business, you don’t need to leave the company to find those opportunities. Having learning be tied to our culture enables internal mobility and growth in a way that is really unique.”

Recommended:

“These books have enriched my understanding of tech leadership, offering new perspectives on challenges I’ve faced and reinforcing essential concepts. While on the job training provides a tremendous opportunity to grow, seeking out additional content is also part of continuous learning. Some of these books cover content that I “know already” but help frame it differently or serve as a reminder of the foundations as my role has evolved. Revisiting these resources periodically helps me stay grounded as I navigate day-to-day challenges, and I’m always on the lookout for new resources to learn from.”

Conclusion: Cultivating Growth at Rapid7

As he reflects on his path, Cathal emphasises how Rapid7 fosters a culture of growth, allowing employees to take active ownership of their career trajectories.

“Before joining Rapid7, I heard a lot about the company’s culture. After nearly three years, I can say it truly sets Rapid7 apart. People here focus not just on their own success but on the success of their colleagues and the collective. This environment fosters trust, encourages open feedback, and provides unique learning experiences—all of which make Rapid7 a place where careers can thrive.”

For those interested in joining the Rapid7 team, you can explore opportunities on our careers page or view all open roles here.

20/20 Cybersecurity: Lessons Learned in 2024 and Strategies for a Stronger 2025

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/11/04/20-20-cybersecurity-lessons-learned-in-2024-and-strategies-for-a-stronger-2025/

20/20 Cybersecurity: Lessons Learned in 2024 and Strategies for a Stronger 2025

With 2024 rapidly coming to a close, many of us here at Rapid7 are taking a step back, reflecting upon the successes and learnings of the last 12 months, and looking ahead to the challenges and opportunities we could jointly face in the year ahead. Of course, we are doing the same for our customers.

For cybersecurity practitioners, 2024 has been nothing short of a rollercoaster ride. As organizations continue to embrace digital transformation at an accelerated pace, the security landscape has shifted, forcing security teams to confront new threats on top of the old and adjust their strategies in real-time.

This year, more than any other, it feels like we’ve witnessed the perfect storm that will forever reshape our industry. Supply chain incidents, sophisticated ransomware attacks, and a global IT outage disrupted critical infrastructure and affected organizations across all sectors and geographies. That’s on top of the backdrop of some of the biggest public data breaches we’ve ever seen. It’s a stark reminder of the ongoing vulnerability of sensitive data and the escalating cost of breaches.

Beyond these headline-grabbing incidents, cybersecurity teams have contended with a growing attack surface driven by the proliferation of IoT devices, an uptick in cloud adoption, and the increasing interconnectivity of systems. Threat actors have capitalized on this complexity, launching more sophisticated, multi-stage attacks that challenge even the most mature security operations centers (SOCs). The sheer volume and diversity of attacks have made it clear: This is not a game of adding more tools to the stack but of refining strategies, fortifying defenses, and focusing on cybersecurity fundamentals.

The Year of Operational Strain and Strategic Reassessment

As cyber threats grew more pervasive and intricate, the demands on security teams reached a breaking point. The year was marked by operational strain, with SecOps teams pushed to their limits to defend against an onslaught of increasingly complex threats. For many organizations, resource constraints — both in terms of personnel and budgets — further compounded the issue, leading to a reactive stance rather than a proactive one. This environment has necessitated a strategic reassessment of how we approach security.

The reality is stark: In 2024, many security professionals found themselves spending more time chasing alerts and parsing through logs than addressing core security challenges. This operational burden has impacted efficiency, morale, and ultimately, the effectiveness of security measures.

Yet, amidst these challenges lies a critical insight. Empowering teams with the right knowledge, tools, and support can dramatically transform outcomes. Security leaders must take command, refocusing on strategies that foster collaboration and transparency while building resilience against a dynamic threat landscape.

Empowering Teams: A New Approach for 2025

Heading into 2025, the need for a shift in approach has never been clearer. This is not merely about layering more technology into an already complex environment. It’s about establishing a partnership that empowers teams to confidently anticipate, pinpoint, and act against threats with precision and clarity. When security professionals are equipped with the right data and expertise, they can reduce the noise, eliminate inefficiencies, and spend more time addressing the strategic priorities that truly matter to their organizations.

Central to this strategy is fostering a culture of trust and collaboration between security teams and other business units. By breaking down silos and establishing shared goals, security leaders can ensure that everyone — from technical stakeholders to the C-Suite — is aligned on what success looks like and how it will be measured. This unified approach, underpinned by reliable data and transparent communication, is key to mitigating risk and optimizing security operations.

Join Us for the 2025 Security Predictions Webinar

To help the security community navigate these evolving challenges and prepare for what’s ahead, Rapid7 is once again hosting its annual 2025 Security Predictions webinar. Featuring our Chief Scientist, Raj Samani, and Vice President of Global Government Affairs and Public Policy, Sabeen Malik, this webinar will explore some of the most pressing issues facing the security community and provide valuable insights into how organizations can better position themselves for the future.

Reflecting on past discussions, we’ve tackled critical themes like talent shortages, public versus private information sharing, and the operationalization of security.

Plan for 2025 with Confidence

Our retrospective on 2024 might feel laden with challenges, yet there is an undeniable silver lining: A unified cybersecurity strategy is within reach. By breaking down organizational silos, fostering a shared vision, and empowering security teams to act with precision and clarity, organizations can take command of their security posture.

At Rapid7, we believe that clarity is power. As we look toward 2025, our mission is to provide that clarity and support, enabling organizations to anticipate, pinpoint, and act on threats with confidence. The lessons of 2024 have taught us that resilience and adaptability are paramount. Now is the time to capitalize on these learnings and put them into practice.

Register Now

Register today and save your seat. Let’s make 2025 the year we take command of the attack surface, reduce operational risk, and set the standard for proactive, efficient, and effective cybersecurity.

Investigating a SharePoint Compromise: IR Tales from the Field

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/10/30/investigating-a-sharepoint-compromise-ir-tales-from-the-field/

Executive summary

Investigating a SharePoint Compromise: IR Tales from the Field

Rapid7’s Incident Response team recently investigated a Microsoft Exchange service account with domain administrator privileges. Our investigation uncovered an attacker who accessed a server without authorization and moved laterally across the network, compromising the entire domain. The attacker remained undetected for two weeks. Rapid7 determined the initial access vector to be the exploitation of a vulnerability, CVE 2024-38094, within the on-premise SharePoint server.

Exploitation for initial access has been a common theme in 2024, often requiring security tooling and efficient response procedures to avoid major impact. The attacker’s tactics, techniques, and procedures (TTPs) are showcased in this blog, along with some twists and turns we encountered when handling the investigation.

Observed attacker behavior

Rapid7 began exploring suspicious activity that involved process executions tied to a Microsoft Exchange service account. This involved the service account installing the Horoung Antivirus (AV) software, which was not an authorized software in the environment. For context, Horoung Antivirus is a popular AV software in China that can be installed from Microsoft Store. Most notably, the installation of Horoung caused a conflict with active security products on the system. This resulted in a crash of these services. Stopping the system’s current security solutions allowed the attacker freedom to pursue follow-on objectives thus relating this malicious activity to Impairing Defenses (T1562).

Zooming out from the specific event to look at the surrounding activity paints a clear picture of the attacker’s intended goal. Shortly before installing Horoung AV, the attacker used Python to install Impacket from GitHub and then attempted to execute it. Impacket is a collection of open-source Python scripts to interact with network protocols, typically utilized to facilitate lateral movement and other post-exploitation objectives. The system’s security tooling blocked the Impacket execution, which led to the download via browser and installation of this AV product to circumvent defenses.

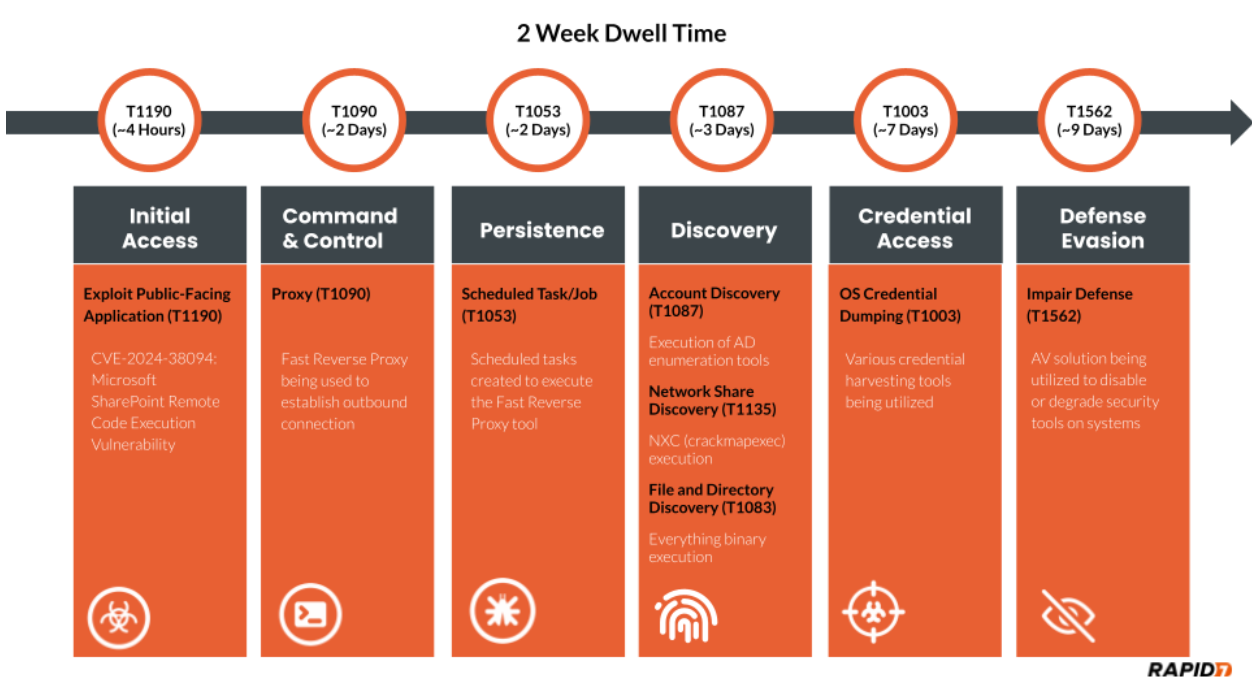
As with many incident response investigations, identified clues are not always chronological, thus requiring a timeline to be constructed to understand the narrative. We must attempt to discover how the attacker compromised the system or accessed the environment in the first place. In this specific investigation, the attacker had a dwell time of two weeks. The attacker’s actions are detailed chronologically in the figure below.

Investigating a SharePoint Compromise: IR Tales from the Field
Figure 1: MITRE Timeline

A great resource for identifying lateral movement involves analysis of authentication event logs from the domain controllers, specifically event ID 4624. Evidence indicated that malicious activity for this compromised Exchange service account involved more than just this single system. The source of unauthorized activity went back a week prior on a domain controller.

Analysis of the domain controller revealed that the attacker used this Exchange service account to authenticate via Remote Desktop Protocol (RDP). The attacker went on to disable Windows Defender Threat Detection (WDTD) on the system and added an exclusion for a malicious binary called msvrp.exe using the GUI. The malicious binary was placed in the C:\ProgramData\VMware\ folder but was not related to VMware. This binary is a tool called Fast Reverse Proxy (FRP), which allows external access to the system through a NAT-configured firewall. The FRP tool requires an .ini file to provide the necessary network configuration to establish an outbound connection. The .ini file’s external IP address has been provided in the Indicators of Compromise (IoCs) table in this blog post. Persistence was established for the FRP via scheduled tasks on the domain controller. Review of the C:\ProgramData\VMware\ folder used by the attacker revealed additional malicious binaries such as ADExplorer64.exe, NTDSUtil.exe, and nxc.exe. These tools were utilized to map the Active Directory environment, gather credentials, and scan systems.

Further analysis of authentication events from the domain controller indicated this malicious activity was sourced from a public-facing SharePoint server. Evidence indicated that the attacker executed Mimikatz, and there were signs of log tampering on the SharePoint server. It also indicated that a majority of system logging was disabled, and several key event log sources were absent during the investigation timeframe. Mimikatz has the ability to clear event logs and disable system logging. These malicious executions were tied to the local administrator account on the system. This would provide the necessary privileges for log tampering on the SharePoint server. However, some logs were spared, such as RDP log evidence. This indicated all authentication for the local administrator account was sourced from the local system to the local system during the in-scope time frame. The authentication information indicated that the potential initial access vector (IAV) would be tied to this SharePoint server. In light of this evidence, Rapid7 dug deeper into potential exploitation of the SharePoint services for an answer.

Rapid7 reviewed available SharePoint inetpub logs and identified the following GET and POST requests indicative of CVE-2024-38094 being exploited from the external IP address 18.195.61[.]200.

POST /_vti_bin/client.svc/web/GetFolderByServerRelativeUrl('/BusinessDataMetadataC atalog/')/Files/add(url='/BusinessDataMetadataCatalog/BDCMetadata.bdcm 
			
POST /_vti_bin/DelveApi.ashx/config/ghostfile93.aspx 

This vulnerability allows for remote code execution (RCE) on systems running Microsoft SharePoint from an external source. The proof-of-concept (PoC) code identified here was observed in available SharePoint log evidence. A great resource that explains the PoC code on Github can be found here. Utilizing this vulnerability, the attacker dropped a webshell on the system. The webshell was called ghostfile93.aspx, which generated numerous HTTP POST requests from the same external IP address tied to the exploit string within log evidence. After several hours of using the webshell, the attacker authenticated into the system using the local administrator account.

Initial access occurred two weeks prior to the start of the investigation. The attacker performed other notable TTPs during the dwell time. These TTPs involved utilizing several binaries to include everything.exe, kerbrute_windows_amd64.exe, 66.exe, Certify.exe, and attempts to destroy third-party backups. The binary everything.exe can index the NTFS file system for efficient searching across files, such as recently used files and network shares. Some of the most notable binaries include 66.exe, a renamed version of Mimikatz, and Certify.exe, which creates an ADFS certificate to utilize for elevated actions within the Active Directory environment. The remaining binary kerbrute_windows_amd64.exe has extensive capability for brute-forcing Active Directory Kerberos tickets. The attacker failed to compromise the third-party backup solution but attempted multiple methods, including access via the browser using compromised credentials and connecting over SSH.

As discussed previously, the installation of external AV products to disable security tooling was an interesting TTP identified during this investigation. Shortly after being blocked for attempted Impacket execution, Rapid7 identified the attacker leveraging an installation batch script called hrsword install.bat. The contents of this script indicate that the Huorong AntiVirus (AV) security solution was being installed. This script involved a service creation called sysdiag to execute the driver file sysdiag_win10.sys, which creates a VBS script execution parameter to execute HRSword.exe. Rapid7 observed this installation causing errors for security products on the system, potentially leading to a scenario in which the service or application would crash. These install files and all IOCs identified during this investigation have been provided in the IOC table contained within this blog.

Rapid7 customers

InsightVM and Nexpose customers can assess their exposure to the Microsoft SharePoint CVE-2024-38094 with authenticated vulnerability checks added in the July 09, 2024 content release.

Rapid7 used Velociraptor during this investigation to allow for remote triage and collection of forensic artifacts on the endpoint. A Velociraptor artifact has been created to hunt for strings related to the public PoC and log evidence identified during the investigation. The artifact can be found within the Rapid7 Labs VQL Repo here

InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on behavior related to exploitation of this vulnerability.
Suspicious Commands Launched by Webserver
IIS Launching Discovery Commands
IIS Spawns PowerShell
Attacker Tool – Impacket
Attacker Tool – MimiKatz
Attacker Technique – Hash Dumping With NTDSUtil
Attacker Technique – Clearing Event Logs
Defense Evasion – Disabling Multiple Security or Backup Products

Rapid7 also recommends ensuring that SharePoint is patched to the latest version.

MITRE ATT&CK techniques

Tactic Technique Details
Initial Access Exploit Public-Facing Application (T1190) CVE-2024-38094: Microsoft SharePoint Remote Code Execution Vulnerability
Defense Evasion Impair Defense (T1562) AV solution being utilized to disable or degrade security tools on systems.
Discovery Account Discovery (T1087) Usage of AD enumeration tools
Command and Control Proxy (T1090) Fast Reverse Proxy being used to establish outbound connection
Discovery File and Directory Discovery (T1083) Everything.exe being observed on in-scope systems.
Discovery Network Share Discovery (T1135) nxc.exe being observed on in-scope systems.
Credential Access OS Credential Dumping (T1003) Various credential harvesting tools observed on in-scope systems
Persistence Scheduled Task/Job (T1053) Scheduled tasks observed on in-scope systems to execute the FRP tool.

Indicators of Compromise

Attribute Value Description
Filename and Path c:\users\Redacted\documents\everything-1.4.1.1024.x86\everything.exe Binary to locate files
SHA256 d3a6ed07bd3b52c62411132d060560f9c0c88ce183851f16b632a99b4d4e7581 Hash for everything.exe
Filename and Path c:\programdata\vmware\66.exe Renamed mimikatz.exe
SHA256 61c0810a23580cf492a6ba4f7654566108331e7a4134c968c2d6a05261b2d8a1 Hash for mimikatz.exe
Filename and Path c:\programdata\vmware\certify.exe Creates an ADFS certificate to utilize for elevated actions within the Active Directory environment.
SHA256 95cc0b082fcfc366a7de8030a6325c099d8012533a3234edbdf555df082413c7 Hash for certify.exe
Filename and Path c:\programdata\vmware\kerbrute_windows_amd64.exe Used to perform Kerberos pre-auth brute forcing.
SHA256 d18aa84b7bf0efde9c6b5db2a38ab1ec9484c59c5284c0bd080f5197bf9388b0 Hash for kerbrute_windows_amd64.exe
Filename and Path c:\programdata\vmware\msvrp.exe Fast Reverse Proxy tool for allowing external access to the system through a NAT configured firewall.
SHA256 f618b09c0908119399d14f80fc868b002b987006f7c76adbcec1ac11b9208940 Hash for msvrp.exe
Filename and Path c:\programdata\vmware\nxc.exe Newer version of the CrackMapExec Network Pentesting tool.
SHA256 95cc0b082fcfc366a7de8030a6325c099d8012533a3234edbdf555df082413c7 Hash for nxc.exe
Filename and Path c:\programdata\vmware\adexplorer64.exe Active Directory Enumeration Tool
SHA256 e451287843b3927c6046eaabd3e22b929bc1f445eec23a73b1398b115d02e4fb Hash for adexplorer64.exe
Filename and Path c:\users\Redacted\documents\h\hrsword install.bat Component of Huorong AV
SHA256 1beec8cecd28fdf9f7e0fc5fb9226b360934086ded84f69e3d542d1362e3fdf3 Hash for hrsword install.bat
Filename and Path c:\users\Redacted\documents\h\hrsword.exe Component of Huorong AV
SHA256 6ce228240458563d73c1c3cbbd04ef15cb7c5badacc78ce331848f5431b406cc Hash for hrsword.exe
Filename and Path c:\Windows\System32\drivers\sysdiag_win10.sys System driver component of Huorong AV
SHA256 acb5de5a69c06b7501f86c0522d10fefa9c34776c7535e937e946c6abfc9bbc6 Hash for sysdiag_win10.sys
Log-Based IOC POST /_vti_bin/client.svc/web/GetFolderByServerRelativeUrl(‘/BusinessDataMetadataC atalog/’)/Files/add(url=’/BusinessDataMetadataCatalog/BDCMetadata.bdcm POC code identified in SharePoint logs.
Log-Based IOC POST /_vti_bin/DelveApi.ashx/config/ghostfile93.aspx Webshell identified within SharePoint logs.
IP Address 54.255.89[.]118 IP address from .ini file for Fast Reverse Proxy tool
IP Address 18.195.61[.]200 Source IP address from exploitation and webshell communications

7 Rapid Questions on our Belfast Placement Programme: Orla Magee and Paddy McDermott

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/10/18/7-rapid-questions-on-our-belfast-placement-programme-orla-magee-and-paddy-mcdermott/

7 Rapid Questions on our Belfast Placement Programme: Orla Magee and Paddy McDermott

Ever wonder what it’s like to be an intern at Rapid7 in Belfast?

Software Engineers Orla Magee and Paddy McDermott share what the interview process looked like for them, along with impactful projects and advice for others exploring Rapid7’s Placement Programme.

What was the interview process like for the Placement Programme?

Paddy: The interview process for Rapid7’s Placement Programme was well structured and welcoming. It consisted of two parts, a one-on-one chat focusing on cultural alignment, and a technical interview with programming questions and a puzzle to solve. The interviewers were approachable, which helped me feel at ease. I felt as though they struck a good balance, assessing my skills without overwhelming me with information and questions. It felt like a genuine attempt to get to know me as a person and assess my skills, rather than just ticking boxes.

Orla: From the start, the talent acquisition team was friendly and communicative, keeping me well-informed about each stage. The interviewers seemed genuinely interested in getting to know me as a person, highlighting that being yourself is crucial in this process. Overall, the interview experience reflected positively on Rapid7’s commitment to finding well-rounded individuals who can contribute both technically and culturally to their team, which made me feel at ease and excited for an opportunity to work at Rapid7.

What initially stood out to you about Rapid7?

Paddy: What stood out to me about Rapid7 was the genuine connection I felt with the people I met during the interview process. The interviewers were engaging and approachable, which gave me a strong sense of the company’s collaborative culture. Another thing that caught my attention was Rapid7’s commitment to growing new talent. This became clear when I attended an event specifically for intern applicants, where I got to experience the company’s welcoming atmosphere firsthand. A mix of friendly people, a learning-focused environment and the opportunity for significant professional growth really made Rapid7 stand out as an ideal place to begin my career.

What was the learning curve like coming into Rapid7 as a student, and what resources or tools did you have to navigate that?

Orla: Transitioning from university to working at Rapid7 as a student came with a significant learning curve. In university, I was used to working independently on projects. At Rapid7, I had to adapt to collaborating as part of a team. This shift required developing my communication skills and learning to work effectively with others. Additionally, the codebase was much bigger and more complex than the smaller-scale projects I had worked on in university. To help navigate these challenges, I was paired with a mentor at the start of my internship, who was instrumental in developing my technical abilities and helping me adjust to working in a professional environment. Alongside my mentor, my team members were always willing to offer assistance and guidance, creating a supportive atmosphere that facilitated my learning and growth. This combination of mentorship and team support was crucial in helping me overcome the learning curve and successfully adapt to a new work environment.

Can you share a memorable project or experience?

Paddy: One of my most memorable achievements during my placement was developing a full-stack status page. This project was particularly significant as it served a real, practical purpose within the company. The status page I created was designed to alert on outages and display the health of various components of our team’s pipeline. This tool was used beyond our team, and was shared internally across different parts of the company. This project allowed me to greatly expand my full-stack development skills in a meaningful way. It was rewarding to see something I built from the ground up being actively used to improve monitoring and communication about our pipeline’s status.

What advice would you give someone looking to land a Placement with Rapid7?

Orla: Take advantage of intern nights, held at the office, as these events offer a unique glimpse into Rapid7’s culture and team dynamics. These events are great opportunities to network and build connections with current staff members, potentially giving you an insider’s perspective on the company.

Paddy: My main advice would be to be yourself throughout the whole process as this will really   help you connect with the interviewers and showcase your true potential. Also, make sure to demonstrate a strong willingness to learn, as Rapid7 values candidates who are eager to grow and take on new challenges.

What were some of your biggest fears coming in, And how did that compare to reality?

Orla: When I started my internship at Rapid7, my main concern was that my technical skills might not measure up to those of my peers. I worried about potentially struggling to contribute meaningfully to the team, but my real experience showed that these worries were unnecessary. From day one, I was met with a welcoming and supportive environment. My colleagues were not only understanding of my position as an intern but were also genuinely enthusiastic about helping me develop my skills. They took the time to walk me through their current projects, providing valuable context and insights that helped me quickly get up to speed. My initial uncertainty was replaced with excitement for the opportunity to learn and contribute, and the reality of the internship far exceeded my expectations.

How has your placement experience prepared you for a successful career?

Paddy: Overall, the placement has given me a mix of technical growth, hands-on experience and professional development creating a strong foundation for my future in tech. I’ve learned many new programming languages with guidance from experienced colleagues. Working in a live production environment has equipped me with real-world skills and experiences. Presenting demos has boosted my confidence in public speaking and taught me how to communicate technical concepts effectively. I’ve built connections and friendships with coworkers which has made the work environment enjoyable and allowed me to start to form a professional network that will be valuable in my career.

Interested in learning more about the Placement Programme, or additional emerging talent programmes at Rapid7? Click here to explore our offerings and view open jobs.

Root Access for Data Control: A DEF CON IoT Village Story

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/10/16/root-access-for-data-control-a-def-con-iot-village-story/

Root Access for Data Control: A DEF CON IoT Village Story

Every year, Rapid7 is a presenter at DEF CON’s IoT Village, sharing in-depth insight and expertise into the hacking of all things Internet of Things. This year, our perennial IoT hacking presenter, Principal Security Researcher, IoT, Deral Heiland, along with Rapid7 pentest team members, showed attendees many methods of extracting firmware from IoT devices and manipulating the systems in the name of control and operations.

Extracting firmware without the use of destructive means can be difficult and in some cases impossible. However, Deral went deep with IoT Village attendees, presenting a live hands-on exercise each attendee in the room could interact with. It was an enlightening and productive presentation. But we are aware not everyone could make it to DEF CON 32 this year.

Which is why we’ve transformed the presentation into a handy whitepaper. Deral has gone step-by-step through the exercise, and even improved upon it in some cases (so even if you were in the room, there’s likely even more for you to get from it). While DEF CON 32 may be firmly in the rear-view mirror, the hacking carries on. And if you missed DEF CON, or Deral’s presentation, you have another chance to learn and take part in the exercise.

To check out the whitepaper, please click here. And if you’d like to learn more about Deral’s previous IoT Village presentations (he’s done a lot of them), many live right here on the blog.

Test Driving a New Benefit Programme in Belfast

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/10/16/test-driving-a-new-benefit-programme-in-belfast/

Test Driving a New Benefit Programme in Belfast

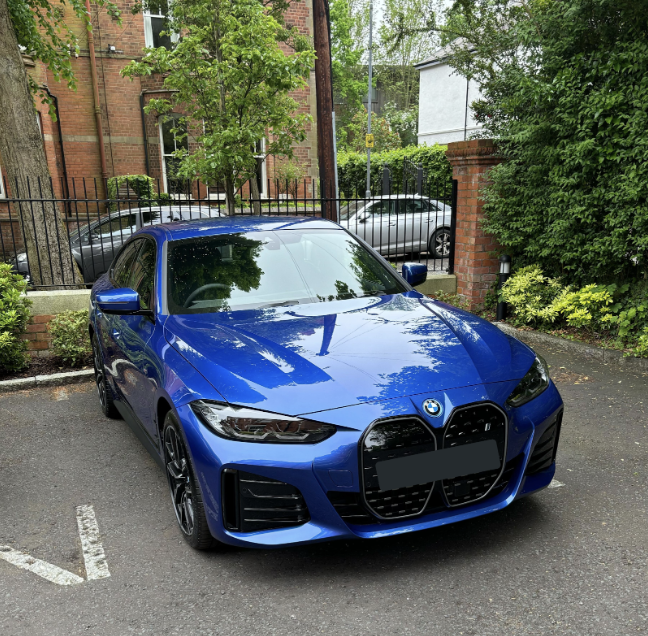
When most people think about benefits packages at work, what typically comes to mind are things like healthcare programmes, financial stipends, or wellbeing incentives. For Stephen, one benefit he uses on a daily basis comes on four wheels.

Rapid7’s electric vehicle scheme was rolled out in late 2023 for Belfast employees. The programme enables employees to lease an electric car via their employer and pay for it on a salary sacrifice basis, offering substantial tax and national insurance savings.

“I kept reading about the program and thinking – is it really this simple? What’s the catch?” said Stephen Gallagher, a Lead Product Manager who received his new electric BMW this past May. “The more I learned about the process and understood what that pre-tax payment would be vs. paying for a vehicle on my own, it was really a no brainer.”

The unique offering also contributes to the company’s sustainability goals by making electric vehicles more accessible, thanks to the pre-tax salary sacrifice. “I’ve worked for some other big tech companies in Belfast, but I’ve never seen this as a company offering. It definitely gives me a great sense of pride to work for Rapid7, and I feel motivated to do well for a company that takes care of employees in such a unique way.”

Test Driving a New Benefit Programme in Belfast

“The program provides employees with make and model options based on different salary levels to ensure the monthly payment is reasonable. Once an employee enrolls and selects a vehicle, our vendor sources it and coordinates delivery. Employees don’t pay anything until the vehicle is delivered.” Says Karen Hendry, Senior Benefits Manager. “I’ve watched employees go through the process, and I’m excited to have just taken ownership of a car myself through the programme!”

In addition to a competitive monthly payment, the program also eliminates the need for down payments, dealer fees, maintenance, or separate insurance fees as the offering is all inclusive. Stephen shared more on his recent experience by adding “I recently got a scratch on the car, so it’s been in the shop to get repaired. All I had to do was reach out to our vendor, and they got me in touch with a repair shop and coordinated everything for me”.

“As a benefits team, we are always evaluating our offerings and looking for ways to bring value to our employees through unique programmes. It’s exciting to see something new like this take off successfully in Belfast”

Learn more about Rapid7 in Belfast here.

Proactive Visibility Is Foundational to Strong Cybersecurity

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/30/proactive-visibility-is-foundational-to-strong-cybersecurity/

Proactive Visibility Is Foundational to Strong Cybersecurity

Authored by Guest IDC Blogger: Michelle Abraham

Exposures are more than CVEs, so organizations need to move beyond the traditional thinking of vulnerability management to a holistic view. Part of that view must be greater visibility into devices, users, applications, and all the digital infrastructure connected to an organization’s environment. Gaps in that view create risk exposure. Organizations must proactively identify anything that presents a risk to determine whether to act.

Solutions that improve visibility discover assets, aggregate all asset data in one place, and enrich that data to understand the relationships between users, assets, and applications. These cybersecurity asset management systems connect to other security tools in the IT environment to gather their telemetry on what they see and the communications they have. The data from these connections can overlap and be duplicative, so the system needs to deduplicate the data to render it useful for security.

Attack surface management (ASM) adds to the visibility by showing an external view of the digital estate, allowing security teams to see the view attackers have from outside their environment. Attack surfaces have expanded rapidly and often involve a hybrid multicloud environment and SaaS applications, including GenAI. Identifying unknown internet-exposed assets that provide a pathway to critical data is essential to managing risk.

Knowing what constitutes the environment that must be secured should be the foundation upon which the rest is built. Finding part of shadow IT helps with a portion of the problem but does not solve it. Alternatively, investigating assets that are falsely attributed to an organization wastes time. It is common for organizations to find 15%–30% more assets when they adopt security tooling for asset discovery.

Solutions need to bring together many sources of data — both first- and-third-party internal and external views of the environment — for a single source of truth about an organization’s digital estate. The assets must include both cloud and on-premises resources to optimize the organization’s security posture for its risk tolerance level. Solutions should also be capable of discovering unknown users and the unsanctioned use of IT resources and applications, which are additional risk exposures. The addition of threat and vulnerability intelligence helps security team’s understand the exploitability of the exposure so the most critical issues can be prioritized for remediation.

The flow of information from these tools requires continuous updating because threat actors can seize on any gap, whether recent or present from the beginning. The data shown should include asset configuration and asset criticality in the context of the business, such as whether the asset supports key business applications or has access to sensitive datasets. Knowing who owns an asset is also vital information so that security and IT know who is responsible for fixing a problem when it arises, particularly if ownership resides outside these two areas. Asset ownership will drive accountability for remediation programs and campaigns.

With a bi-directional connection to the configuration management database (CMDB), a solution that combines Cyber Asset Attack Surface Management (CAASM) and ASM further aligns the entire organization with the most updated information. It augments the CMDB to help with asset lifecycle management because end-of-life devices that no longer receive updates pose a risk. Systems should also be able to track and report on additional exposures, such as expiring certificates or unknown certificate issuers.

A map of asset and user relationships helps visualize the paths that attackers can take to traverse the network for lateral movement in the environment to get to the organization’s crown jewels. CAASM and ASM output must be more than just a dump of data from various tools; the data must be easy to query, with actionable insights that help the organization reduce risk. Matching the data from assets provides teams reacting to threats with complete context regarding assets to aid their investigation and remediation efforts. The remediation process is easier when there are recommended actions as well as integrations with ticketing systems or automation platforms that inform asset owners of issues as well as track the status of the patch or mitigation.

Consider CAASM and ASM as foundational elements to a strong, mature security program that is aware of its entire digital estate. This visibility eliminates one of the ways attackers take organizations by surprise, thereby reducing overall risk.

Message from the Sponsor

The dynamic nature of modern IT environments demands a proactive and continuous approach to exposure management. Doing so requires real-time visibility into your entire digital estate and the exposures that leave your organization vulnerable to compromise. By enriching unified internal and external views of your attack surface with real-world threat intelligence and context from your entire tooling ecosystem, teams have the situational awareness needed to prioritize response efforts and accelerate mean time to remediation. Watch this on-demand demo to learn how Rapid7 Exposure Command can help transform your security program and allow you to take command of your attack surface.

Multiple Vulnerabilities in Common Unix Printing System (CUPS)

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/26/etr-multiple-vulnerabilities-in-common-unix-printing-system-cups/

Multiple Vulnerabilities in Common Unix Printing System (CUPS)

On Thursday, September 26, 2024, a security researcher publicly disclosed several vulnerabilities affecting different components of OpenPrinting’s CUPS (Common Unix Printing System). CUPS is a popular IPP-based open-source printing system primarily (but not only) for Linux and UNIX-like operating systems. According to the researcher, a successful exploit chain allows remote unauthenticated attackers to replace existing printers’ IPP URLs with malicious URLs, resulting in arbitrary command execution when a print job is started from the target device.

The vulnerabilities disclosed by the researcher are:

  • CVE-2024-47176: Affects cups-browsed <= 2.0.1. The service binds on UDP *:631, trusting any packet from any source to trigger a Get-Printer-Attributes IPP request to an attacker-controlled URL.
  • CVE-2024-47076: Affects libcupsfilters <= 2.1b1. cfGetPrinterAttributes5 does not validate or sanitize the IPP attributes returned from an IPP server, providing attacker-controlled data to the rest of the CUPS system.
  • CVE-2024-47175: Affects libppd <= 2.1b1. The ppdCreatePPDFromIPP2 API does not validate or sanitize the IPP attributes when writing them to a temporary PPD file, allowing the injection of attacker-controlled data in the resulting PPD.
  • CVE-2024-47177: Affects cups-filters <= 2.0.1. The foomatic-rip filter allows arbitrary command execution via the FoomaticRIPCommandLine PPD parameter.

According to the researcher’s disclosure blog, affected systems are exploitable from the public internet, or across network segments, if UDP port 631 is exposed and the vulnerable service is listening. CUPS is enabled by default on most popular Linux distributions, but exploitability may vary across implementations. As of 6 PM ET on Thursday, September 26, Red Hat has an advisory available noting that they consider this group of vulnerabilities of Important severity rather than Critical.

Mitigation guidance

We expect patches and remediation guidance to be forthcoming from affected vendors and distributions over the next few days. While the vulnerabilities are not known to be exploited in the wild at time of disclosure, technical details were leaked before the issues were released publicly, which may mean attackers and researchers have had opportunity to develop exploit code. We advise applying patches and/or mitigations as soon as they are available as a precaution, even if exploitability is more limited in some implementations.

Additional mitigation guidance:

  • Disable and remove the cups-browsed service if it is not necessary
  • Block or restrict traffic to UDP port 631

Rapid7 customers

InsightVM and Nexpose customers will be able to assess their exposure to these CVEs with authenticated checks that look for affected CUPS packages on UNIX-based systems. These checks are expected to be released in a second content release this evening (ETA 10 PM ET on Thursday, September 26).

We expect to update with additional checks in the coming days as vendors release fixes and more information.

Rapid7 Recognized in Forrester’s 2024 Attack Surface Management (ASM) Wave Report

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/24/rapid7-recognized-in-forresters-2024-attack-surface-management-asm-wave-report/

Rapid7 Recognized in Forrester’s 2024 Attack Surface Management (ASM) Wave Report

This week, Rapid7 was recognized as a Contender in Forrester’s 2024 Attack Surface Management (ASM) Wave report. We’re proud to have been selected for inclusion in the report, reflecting a continued dedication to enabling customers to monitor 100% of their attack surface in real-time, and proactively mitigating exposures that leave their organizations susceptible to compromise.

Since Forrester’s initial assessment earlier this year, we’ve further extended our investments in this space, announcing the acquisition of Noetic Cyber, a market-leading cyber asset attack surface management (CAASM) vendor, and subsequently launching the Command Platform with attack surface management – and our new Surface Command product – as the foundation.

Modern business dynamics and an ever-evolving threat landscape makes successful data management a daunting challenge. This leads to a majority of organizations not having a strong grasp on their true attack surface.

  • Teams have accumulated numerous point solutions to try to keep pace with business growth and adapt to their changing environment.
  • Practitioners are consumed by assuming the role of a system integrator, trying to connect a myriad of different solutions that were never intended to be interoperable.
  • This lack of connectivity makes it impossible to get the context and clarity needed to actually make sense of data, know what to prioritize, and where to focus.

Attackers are able to exploit this data sprawl – lurking in mountains of data and betting on your inability to detect them and identify the insights that matter before it’s too late. We recognize that teams need a new path forward, and we are excited to support our customers through this next era of security with our Command Platform.

Establishing A Strong Foundation to Transform Vulnerability Management into a Proactive, Continuous Exposure Management Process

As cyber threats continue to grow in complexity, the traditional approach to Vulnerability Management (VM) must evolve. Static scanning and isolated patching efforts are no longer sufficient in the face of sophisticated attackers who exploit even the smallest gaps in security. Organizations need to adopt a more dynamic, integrated approach to exposure management – one that is continuous, context-aware, and capable of adapting to the sprawling attack surface and shifting threat landscape.

Rapid7 is uniquely positioned to support your organization’s evolution toward a more holistic and continuous process designed to continuously assess, prioritize, and remediate threats across an organization’s entire attack surface. Surface Command is built to provide the comprehensive visibility and actionable insights necessary for effective threat exposure management. Integrating data from across your entire environment – whether it’s on-premises, in the cloud, or somewhere in between – customers are able to see and understand risks in their full context.

With Rapid7, you’re not just getting another vulnerability or attack surface management tool; you’re gaining a partner that helps you elevate your entire security strategy. Our platform’s ability to aggregate and correlate data from different data sources ensures you have a complete, accurate picture of your threat landscape that you can trust. Moreover, our advanced querying capabilities allow you to quickly identify and focus on the most critical risks, enabling timely and precise remediation efforts.

Surface Command stands out in a few ways:

  • Unified Internal and External Attack Surface Visibility: Monitor your attack surface from the inside out with a dynamic asset and identity inventory alongside continuous external scans that provide an adversary’s perspective.
  • Vendor Agnostic Approach: Aggregate all data from your internal and external environments as well as your entire technology ecosystem into a unified asset model.
  • Powerful Search and Analytics: Slice and dice your data however you see fit, with powerful querying capabilities that help you find the needle in the haystack.
  • Seamless Integration and Remediation Workflows: Quickly get relevant asset insights, risk context and initiate remediation workflows all from one place.

This comprehensive visibility and contextual prioritization empowers your security team to shift from a reactive to a proactive posture, transforming your vulnerability management program into a robust, continuous defense mechanism.

Proactively Mitigate Exposures from Endpoint to Cloud

Exposure Command builds off the complete environment visibility powered by Surface Command – ingesting high-fidelity asset data from proprietary and third-party sources, automatically aggregating and correlating that data into an up-to-date asset inventory and topology map. Our powerful querying capabilities allow you to easily adjust your scope and drill into the details you need to spot control gaps, non-compliance and extinguish risk across your hybrid environment.

The platform goes beyond monitoring and asset inventory mapping, enriching telemetry with compliance and risk findings from Rapid7’s entire set of exposure management capabilities. With  hybrid vulnerability management, comprehensive cloud security, and web application testing in one complete solution, security teams can shift from reactive to proactive to stay ahead of adversaries.

Exposure Command extends the power of Surface Command with:

  • Pinpoint and Mitigate Vulnerabilities Everywhere: Automatically prioritize vulnerabilities across your hybrid environment based on exploitability and potential impact.
  • Monitor Effective Access and Enforce Least Privilege Access: Analyze all roles and identities across your clouds to help eliminate excessive permissions and enforce LPA at scale.
  • Proactively Mitigate Exposures in Cloud-native Apps: Avoid risk before it reaches production with IaC and web app scanning that gives actionable feedback to devs where they work.
  • Spot Avenues for Attackers to Traverse Your Cloud Network: Visualize interconnected resources and uncover paths for attackers to move laterally across your environment with attack path analysis.

With these powerful capabilities, Exposure Command allows teams to continuously assess their attack surface, validate exposures and confidently take action with remediation guidance that takes into account existing downstream controls and the blast radius of a potential compromise.

Interested in Learning More About Exposure Command?

If you’re interested in diving deeper into how Rapid7 can help transform your security operations, be sure to check out our recent webcast with Jon Schipp, Sr Dir. Product Management, and Thomas Green, Sr Security Solutions Engineer during which they discuss key strategies for leveraging Exposure Command to stay ahead of today’s evolving threats.

Three Recommendations for Creating a Risk-Based Detection and Response Program

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/24/three-recommendations-for-creating-a-risk-based-detection-and-response-program/

Three Recommendations for Creating a Risk-Based Detection and Response Program

It should come as little surprise to most security professionals that keeping pace with the evolution of threat actors has become harder and harder. Maintaining visibility into the threat landscape and on top of external risk vectors is more than a matter of incorporating more point solutions. It takes a concerted risk-based approach, where the tools you choose are just one leg of the tripod.

In a report released earlier this summer, Gartner analysts offer three recommendations for fostering an environment of risk-based threat detection, investigation, and response that includes a deeper understanding of your organization’s risk profile by more than just the security team. Below are our three main takeaways from the Gartner® 3 Ways to Apply a Risk-Based Approach to Threat Detection, Investigation, and Response.

Takeaway 1: Better alignment and clearer objectives

The need to break silos between teams is a time-honored proposition that holds even more weight now than it ever has. Gartner suggests creating a quorum of business leaders from across the entire organization to be read into the state of your security and the needs going forward. Prioritize accurate and regular reporting of security metrics to build trust and create a consistent atmosphere of effective transparency. This group should be diverse, with decision makers and specialists from core departments. According to Gartner, the goal should be to:

“Allow the business to be part of the conversation and therefore champions of the capability, elevating the security program to a business function rather than an I&O underpinning.”

Takeaway 2: Integrated risk context

Giving incident responders as much information (and the right information) they need to quickly and efficiently respond to threats requires a complex layering of risk information that includes prioritization for the businesses key assets. Gartner recommends the use of cyber-risk information elements directly implemented into an IR program, layering in asset-based and business-risk information that gives responders the context they require to appropriately triage what can often be a large volume of data.

Gartner says:

“Incident responders should have as much information at their disposal as needed to be effective at finding a needle in a haystack.”

Takeaway 3: Fully enriched business context from jump

Too much information can often be as detrimental to a security team as too little. SecOps needs to have access to the right information in the most efficient way possible in order to find the signal through the noise. Gartner recommends reducing investigative delays through enriched information complete with business context (see, they are all connected). This transparency can be accomplished in part through SIEM, CAASM, and threat intelligence tools and a robust vulnerability management program, but it is worth noting that Gartner prioritizes providing the right information, not the most information; hence, utilizing the right tools.

All three of these recommendations combine to create a risk-based approach to detection, investigation, and response that Gartner says: “…organizations can expect to create measurable efficiency gains in threat detection and increase their ability to respond to threats in a timely manner.”

The Gartner® 3 Ways to Apply a Risk-Based Approach to Threat Detection, Investigation, and Response, report goes into even greater detail on the best approaches for implementing a risk-based approach to D&R.

Download the report here.

Gartner, 3 Ways to Apply a Risk-Based Approach to Threat Detection, Investigation and

Response, Jonathan Nunez ,  Pete Shoard , 10 July 2024.

GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the

U.S. and internationally and is used herein with permission. All rights reserved.

High-risk vulnerabilities in common enterprise technologies

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/19/etr-high-risk-vulnerabilities-in-common-enterprise-technologies/

High-risk vulnerabilities in common enterprise technologies

Rapid7 is warning customers about several high-risk vulnerabilities in common enterprise technologies that are attractive potential attack targets for both state-sponsored and financially motivated adversaries. We are advising customers to prioritize remediation for these issues on an expedited basis wherever possible:

  • CVE-2024-41874: Critical remote code execution vulnerability in Adobe ColdFusion
  • CVE-2024-38812, CVE-2024-38813: Remote code execution and privilege escalation vulnerabilities (respectively) in Broadcom VMware vCenter Server and Cloud Foundation
  • CVE-2024-29847: Critical remote code execution (via deserialization) vulnerability in Ivanti Endpoint Manager (EPM)

Adobe ColdFusion CVE-2024-41874

On September 10, 2024, Adobe published a critical advisory for CVE-2024-41874, an unauthenticated remote code execution issue that occurs as a result of unsafe Web Distributed Data eXchange (“Wddx”) packet deserialization. Rapid7 MDR has previously observed exploitation that targets Wddx for remote code execution; we have also previously observed exploitation of multiple other ColdFusion CVEs.

Affected products and mitigation: Adobe ColdFusion 2023 (update 9 and earlier) and Adobe ColdFusion 2021 (update 15 and earlier) are vulnerable to CVE-2024-41874. The vulnerability is resolved in versions 10 and 16, respectively. For more information, see the vendor advisory.

Broadcom VMware vCenter Server CVEs

On September 17, 2024, Broadcom published an advisory on CVE-2024-38812, a critical heap overflow vulnerability affecting VMware vCenter Server. Successful exploitation of CVE-2024-38812 allows an attacker with network access to the vulnerable server to execute code remotely on the target system. CVE-2024-38813, a local privilege escalation vulnerability, was also reported by the same researchers, making this a full-chain exploit. We are not aware of exploitation in the wild as of September 19, 2024, but vCenter Server is a high-value attack target for ransomware and extortion groups.

Affected products and mitigation: Broadcom VMware vCenter Server 7.0 and 8.0 are vulnerable to CVE-2024-38812 and CVE-2024-38813. Fixes are available as indicated in the vendor advisory. Broadcom also has an FAQ available.

Ivanti Endpoint Manager CVE-2024-29847

On September 10, 2024, Ivanti published a security advisory on CVE-2024-29847, an unsafe deserialization vulnerability in Ivanti Endpoint Manager (EPM) solution. Successful exploitation allows unauthenticated attackers to execute code remotely on target systems. Vulnerability details and proof-of-concept exploit code are available.

Affected products and mitigation: Ivanti Endpoint Manager (EPM) 2022 SU5 (and earlier) and EPM 2024 are vulnerable to CVE-2024-29847. Customers using EPM 2022 can remediate this and other recent vulnerabilities by updating to 2022 SU 6. Per Ivanti’s security advisory, EPM 2024 customers can apply an available security patch while waiting for 2024 SU1, which is yet to be released. See Ivanti’s advisory for the latest information.

Rapid7 customers

InsightVM and Nexpose customers can assess their exposure to Adobe ColdFusion CVE-2024-41874 and Broadcom VMware vCenter Server CVE-2024-28812 and CVE-2024-38813 with vulnerability checks released previously. A vulnerability check for Ivanti EPM CVE-2024-29847 is in development and is expected to be available in tomorrow’s (Friday, September 20) content release.

The Growing Importance of Exposure Management: Our Key Insights from Gartner® Hype Cycle™ for Security Operations, 2024

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/13/the-growing-importance-of-exposure-management-our-key-insights-from-gartner-r-hype-cycle-for-security-operations-2024/

The Growing Importance of Exposure Management: Our Key Insights from Gartner® Hype Cycle™ for Security Operations, 2024

The Gartner® Hype Cycle™ for Security Operations, 2024  was published in late July, and is an interesting look at the dynamic nature of both the threat landscape and the diverse range of technologies that security & risk management (SRM) professionals use to safeguard their organizations.

Understanding the Hype Cycle

Gartner Hype Cycles provide a graphic representation of the maturity and adoption of technologies and applications, and how they are potentially relevant to solving real business problems and exploiting new opportunities. Over 90 Hype Cycles are published per year. Hype Cycles provide a snapshot of the relative market penetration, maturity and benefit of innovations within a certain segment, such as a technology area or business market. This Hype Cycle helps security and risk management leaders strategize and deliver SecOps capability and functions.

What we think are key themes from this year’s Hype Cycle for SecOps

The 2024 Hype Cycle has seen some notable additions and consolidations, particularly around the rapidly-evolving Threat Exposure Management (TEM) market, as existing vulnerability assessment and management approaches mature to support the Continuous Threat Exposure Management (CTEM) framework. In the report Gartner defines CTEM as “a program helping organizations to improve their maturity when they govern and operationalize the five recommended phases of exposure management: scoping, discovery, prioritization, validation and mobilization.’”

Three new profiles reflect this evolution:

  • Threat Exposure Management – This is intended to help organizations answer the question, “ow exposed are we?” It extends traditional approaches to vulnerability management to focus on risk reduction across a much wider potential attack surface, including cloud, SaaS applications and the third-party supply chain.

    Today,many organizations currently have a siloed approach to exposure management across many different domains — external, vulnerability scanning, penetration testing — and are struggling to keep up with the pace of environmental change.

    Gartner rates the potential benefit of Threat Exposure Management as ‘transformational’ and states that organizations should ‘employ proper governance and repeatability to make their threat exposure management programs continuous.’

  • Exposure assessment platforms (EAPs) – This is a new category with a ‘high’ benefit rating from Gartner. In the report, Gartner states that EAPs ‘continuously identify and prioritize exposures, such as vulnerabilities and misconfigurations, across a broad range of asset classes. They natively deliver or integrate with discovery capabilities, such as assessment tools that enumerate exposures like vulnerabilities and configuration issues, to increase visibility.’

    Gartner has removed both vulnerability assessment (VA) and vulnerability prioritization technologies (VPT) from this year’s Hype Cycle, stating that they have been ‘subsumed into exposure assessment platforms.’

    We believe that a potential benefit of EAPs is to provide better insights into high-risk exposures, which could allow organizations to prevent security incidents and breaches. They can also improve operational efficiency by providing centralized visibility of assets and exposures, supporting risk scoring reporting and trend analysis across the organization.

    Rapid7 is named as a Sample Vendor for EAP in this latest report.

  • Adversarial exposure validation – The third new category related to exposure management covers the validation pillar of a CTEM program. As noted in the report, “Adversarial exposure validation technologies offer offensive security technologies simulating threat actor tactics, techniques, and procedures to validate the existence of exploitable exposures and test security control effectiveness. Within this profile, Gartner has consolidated breach attack simulation and autonomous penetration testing and red teaming. “
    Gartner recommends that security and risk leaders should ‘Integrate existing attack simulation and penetration testing scenarios into an adversarial exposure validation roadmap, as part of a shift from vulnerability management to a CTEM program.’

As well as these new categories, we also see movement among some of the existing technologies that can support CTEM initiatives – notably Cyber Asset Attack Surface Management (CAASM), External Attack Surface Management (EASM) and Digital Risk Protection Services (DRPS).

Both EASM and DRPS are in the ‘Trough of Disillusionment’ on this year’s Hype Cycle.  Gartner notes, “SRM leaders are reevaluating the value they’re getting from technologies in the trough, often having to reinforce their justification for budgets. For example:[…] Enterprises were unprepared to consume and operationalize service output (digital risk protection services, external attack surface management, ITDR).

CAASM has moved from ‘Innovation Trigger’ to the ‘Peak of Inflated Expectations’, reflecting the growing demand from enterprises to gain better visibility of their attack surfaces. CAASM helps provide more comprehensive visibility into assets by consolidating asset and exposure information into a holistic view. Noetic Cyber, a recent acquisition of Rapid7, is also a Sample Vendor for CAASM.

Rapid7’s vision for Exposure Management

Rapid7 recently announced the availability of Exposure Command and Surface Command, the first two solutions launched on the new Command Platform. Surface Command provides 360-degree visibility across the internal and external environment by bringing together EASM and CAASM in a single solution, enabling security teams to view and prioritize high-risk assets across their extended environments.

Building on the unparalleled visibility provided by Surface Command, Exposure Command expands traditional vulnerability management programs with insights and context from vulnerability, cloud and application security tools, establishing a single, consolidated platform for exposure management across the organization.

The Growing Importance of Exposure Management: Our Key Insights from Gartner® Hype Cycle™ for Security Operations, 2024

This centralized point of exposure management allows security leaders to prioritize based on the overall risk to the business, understand complex attack paths across the cloud and on-premise environments, and surface the top areas teams need to focus on and while elevating the mitigation activities that would have the largest impact in reducing the overall risk score of your environment.

We believe that these new capabilities align well with the Gartner concept of exposure assessment platforms and the overall requirements of a threat exposure management program. To understand more about Rapid7’s approach to attack surface and exposure management, you can find out more here.

Gartner, Hype Cycle for Security Operations, 2024, July 2024.
GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally, and HYPE CYCLE is a registered trademark of Gartner, Inc. and/or its affiliates and are used herein with permission. All rights reserved.
Gartner does not endorse any vendor, product or service depicted in its research publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner’s research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.

CVE-2024-40766: Critical Improper Access Control Vulnerability Affecting SonicWall Devices

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/09/etr-cve-2024-40766-critical-improper-access-control-vulnerability-affecting-sonicwall-devices/

CVE-2024-40766: Critical Improper Access Control Vulnerability Affecting SonicWall Devices

On August 22, 2024, security firm SonicWall published an advisory on CVE-2024-40766, a critical improper access control vulnerability affecting SonicOS, the operating system that runs on the company’s physical and virtual firewalls. While CVE-2024-40766 was not known to be exploited in the wild at the time it was initially disclosed, the SonicWall advisory was later updated to note that “this vulnerability is potentially being exploited in the wild.”

As of September 9, 2024, Rapid7 is aware of several recent incidents (both external and Rapid7-observed) in which SonicWall SSLVPN accounts were targeted or compromised, including by ransomware groups; evidence linking CVE-2024-40766 to these incidents is still circumstantial, but given adversary interest in the software in general, Rapid7 strongly recommends remediating on an emergency basis. Vulnerabilities like CVE-2024-40766 are frequently used for initial access to victim environments.

SonicWall’s advisory indicates CVE-2024-40766 is an improper access control vulnerability “in the SonicWall SonicOS management access and SSLVPN, potentially leading to unauthorized resource access and in specific conditions, causing the firewall to crash.” The vulnerability was added to the U.S. Cybersecurity and Infrastructure Security Agency’s (CISA) list of known exploited vulnerabilities (KEV) on September 9, 2024.

Mitigation guidance

Per the vendor advisory, CVE-2024-40766 affects SonicWall Gen 5 and Gen 6 devices, as well as Gen 7 devices running SonicOS 7.0.1-5035 and older versions.

Affected versions and platforms include:

  • SOHO (Gen 5): 5.9.2.14-12o and older versions affected
  • Gen6 Firewalls: 6.5.4.14-109n and older versions affected (see the advisory for a full list of affected devices)
  • Gen7 Firewalls: SonicOS build version 7.0.1-5035 and older versions affected, but SonicWall recommends installing the latest firmware (see the advisory for a full list of affected devices)

SonicWall recommends restricting firewall management access to trusted sources and/or ensuring firewall WAN management is not accessible from the public internet. They similarly recommend that SSLVPN access is limited to trusted sources, and/or disabling SSLVPN access from the internet.

Rapid7 customers

Our InsightVM engineering team is investigating options for coverage of CVE-2024-40766. We will update this blog with further information no later than 10 AM ET on Tuesday, September 10.