Tag Archives: AWS Cloud WAN

How DeepL keeps closest-exit routing during maintenance with AWS Cloud WAN

Post Syndicated from Guzman Freigedo original https://aws.amazon.com/blogs/architecture/how-deepl-keeps-closest-exit-routing-during-maintenance-with-aws-cloud-wan/

DeepL is a Language AI company that builds written and real-time AI voice translation products used by more than 200,000 business teams worldwide. Its infrastructure spans multiple AWS Regions across Europe, North America and Asia, with hybrid connectivity back to two European data centers.

Taking a single AWS Direct Connect link out of service for planned maintenance is a routine task, but in a multi-Region hybrid network it demands care. DeepL connects its AWS Regions to its data centers through Direct Connect and relies on the default closest-exit egress behavior to keep latency low. For maintenance, the team’s goal was to drain one link while every other Region continued using its local exit.

This post describes how DeepL does this with AWS Cloud WAN and a Direct Connect gateway attached natively to the core network. An AS_PATH prepend on the link being maintained moves only that Region’s traffic to another location, and the other Regions keep their local exit. It also covers the trade-offs, including inter-Region data transfer while a link is drained.

This post is for network architects and cloud platform teams who operate hybrid connectivity at scale, who are evaluating AWS Cloud WAN for global routing, or who are working through Direct Connect traffic engineering across Regions.

DeepL’s hybrid architecture

DeepL runs workloads in multiple AWS Regions, including three in Europe (eu-west-1 in Ireland, eu-central-1 in Frankfurt, and eu-north-1 in Stockholm), two in the United States (us-east-1 and us-west-2), and one in Tokyo (ap-northeast-1). Each Region has multiple virtual private clouds (VPCs) and accounts. On premises, two European data centers connect over a resilient Multiprotocol Label Switching (MPLS) network with dedicated fiber between the sites.

The connectivity design is built for geographic redundancy:

  • Three AWS Direct Connect locations (Dublin, Copenhagen, and Stockholm), each with a hosted 25 Gbps connection through AWS Direct Connect Partner Megaport.
  • An AWS Cloud WAN core network with a core network edge (CNE) in multiple Regions that connects the VPCs and accounts in that Region.
  • One global Direct Connect gateway, linked to all three Direct Connect locations and attached natively to the core network. Native Direct Connect gateway attachments for AWS Cloud WAN have been available since November 2024.
  • The same prefixes advertised from the on-premises routers in both data centers, so that the Direct Connect gateway learns them over all three Direct Connect locations (simplified here to a single /16).

The following diagram shows this architecture.
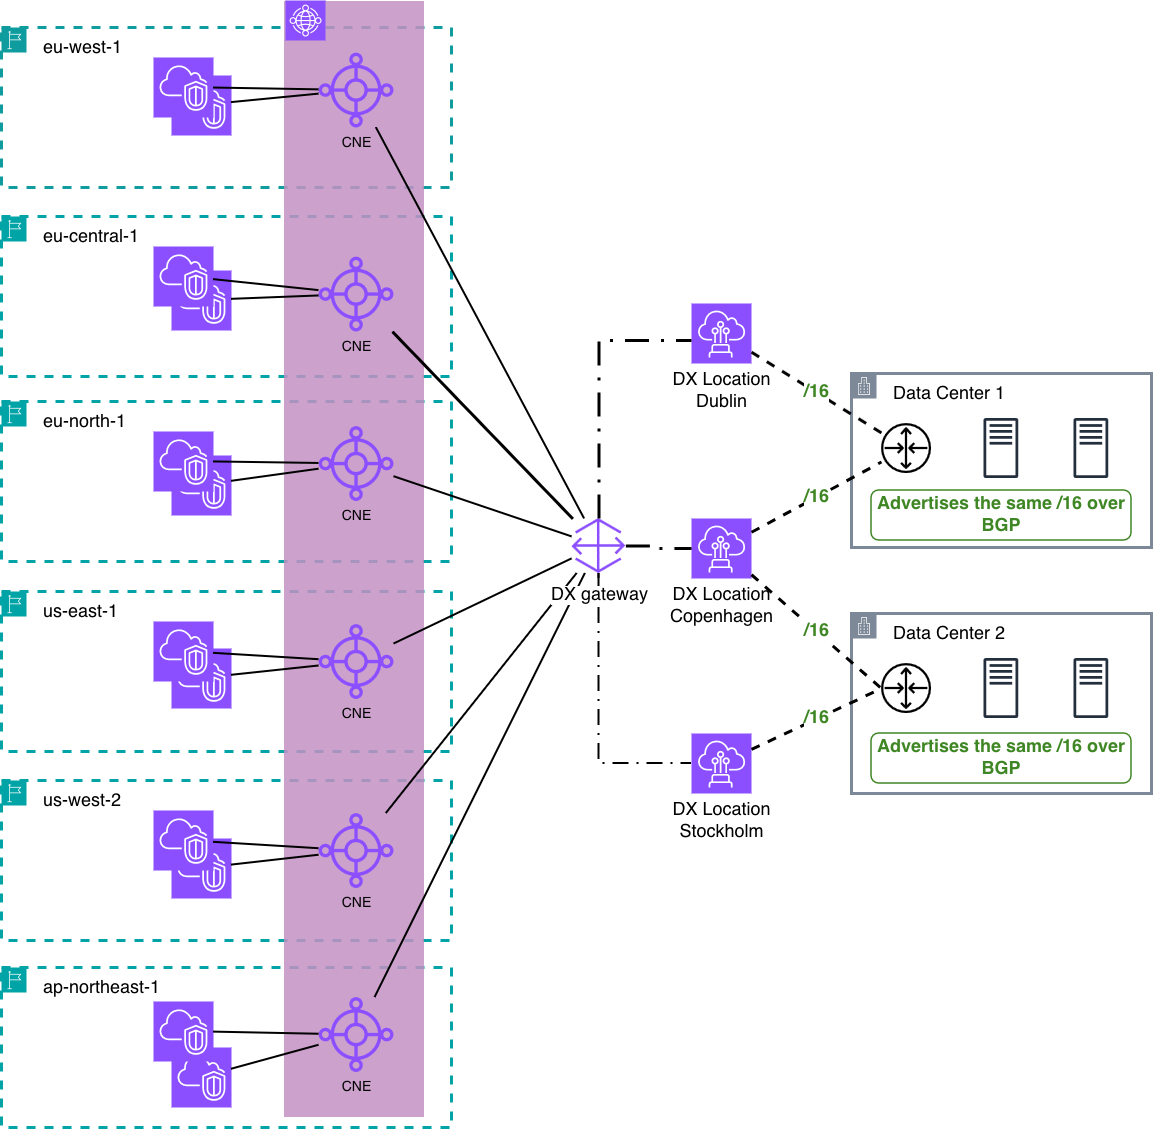
DeepL’s hybrid architecture: AWS Regions connected through an AWS Cloud WAN core network, a Direct Connect gateway, three Direct Connect locations, and two on-premises data centers advertising the same /16

Figure 1: DeepL’s hybrid architecture with AWS Cloud WAN

In steady state, DeepL runs no additional traffic engineering. By default, egress traffic leaves AWS through the Direct Connect location closest to where it originated: traffic from eu-west-1 leaves through Dublin, traffic from eu-central-1 through Copenhagen, and traffic from eu-north-1 through Stockholm. This closest-exit behavior keeps latency low and avoids extra configuration.

DeepL wanted to take the router at one Direct Connect location out of service for a maintenance window. Traffic had to move off that single link while the other two locations kept serving their Regions as before. This is a common requirement for enterprises running multiple Direct Connect locations.

Where the egress decision is made

Before changing any Border Gateway Protocol (BGP) attribute, it helps to know which component makes the egress decision, because that determines which attributes influence it. With Direct Connect attached to an AWS Cloud WAN core network, path selection happens in two places:

  • The Direct Connect gateway.
  • Each core network edge.

Path selection on the Direct Connect gateway

For a prefix reachable through multiple Direct Connect locations, the Direct Connect gateway prefers the path with the highest BGP local preference. By default, AWS sets a medium local preference (community 7224:7200) on the Direct Connect locations associated with the Region where the traffic originates, and a lower value on other locations. Local preference is evaluated before AS_PATH. Setting a local preference community on a prefix applies one ranking to every Region the gateway serves, which suits designs that want the same preferred location everywhere.

The important detail is where local preference sits in the BGP best-path order. When a router has more than one route to the same destination, it walks an ordered list of tie-breakers and stops at the first one that produces a winner. On the AWS side, the first few steps are:

  1. Longest prefix match.
  2. Highest local preference (the closest-exit decision is made here).
  3. Shortest AS_PATH.
  4. Lowest MED.

Local preference is evaluated before AS_PATH. As the Direct Connect documentation states: “Local preference BGP community tags are evaluated before any AS_PATH attribute.” Because the default local preference already selects the Dublin location for eu-west-1 traffic, a longer AS_PATH on the Dublin path doesn’t change the gateway’s choice. The drain takes effect on the core network edge instead, as the next section shows.

Path selection on the core network edge

Each core network edge receives the on-premises path from the Direct Connect gateway with the AS_PATH preserved. Direct Connect BGP communities are only relevant to the Direct Connect gateway and don’t influence core network routing decisions. Each edge also learns the same prefix from its peer edges across the core network, and each of those paths is one AS hop longer because the peer edge adds its own autonomous system number (ASN). The core network edge evaluates AS_PATH length first, so by default each edge prefers the path through the Direct Connect gateway instead of the path from a peer edge. For the three European Regions in DeepL’s environment, that is the path through the Region’s local Direct Connect location. See Direct Connect gateway attachments in AWS Cloud WAN.

The following diagram shows how the eu-west-1 core network edge selects its exit in steady state.
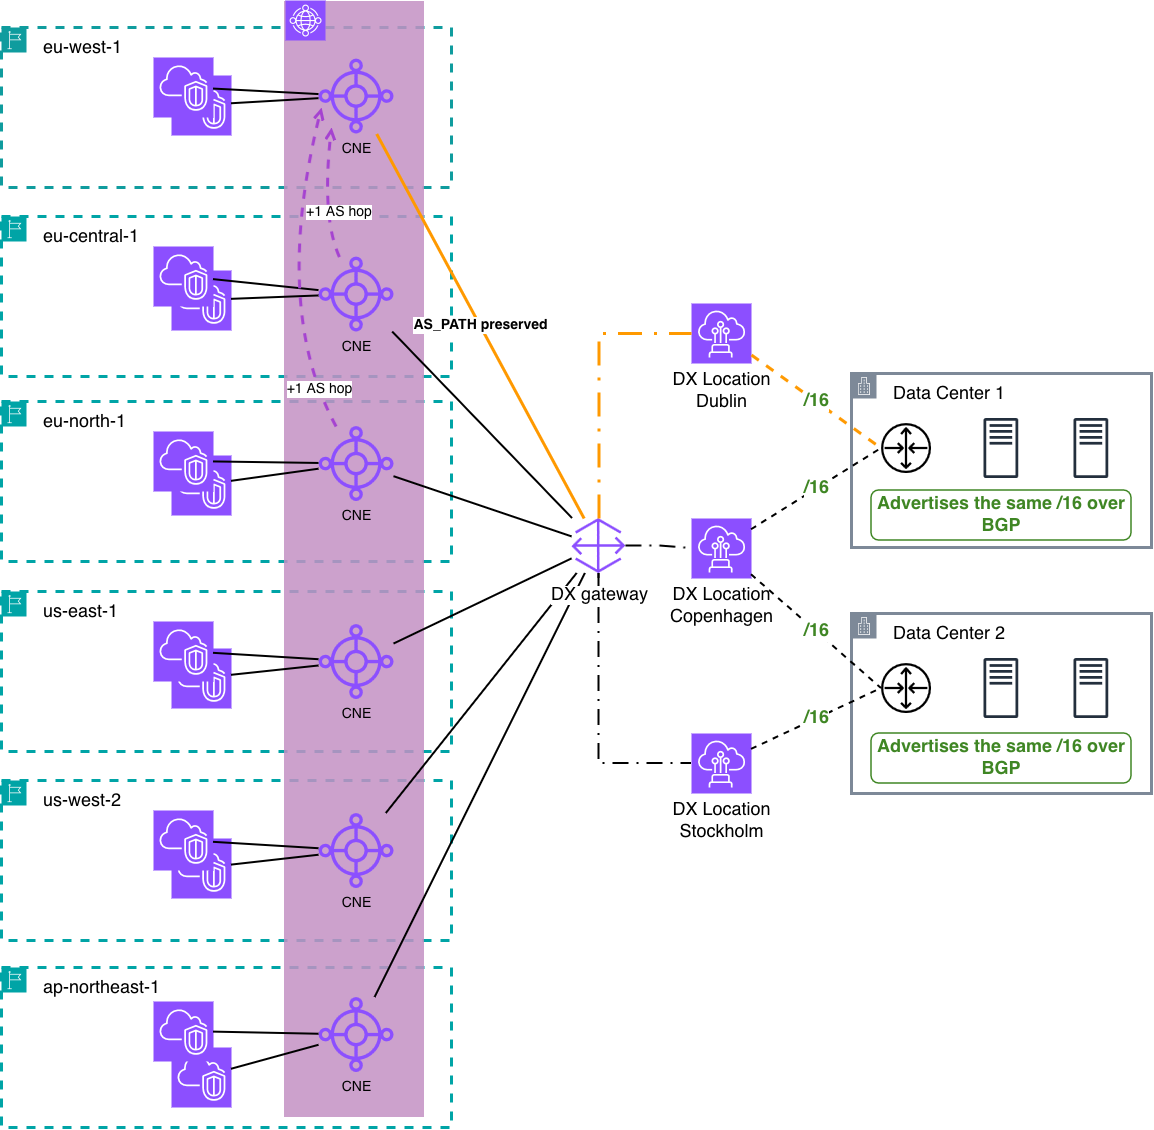
The eu-west-1 core network edge receives the Dublin path from the Direct Connect gateway and a one-AS-hop-longer path from peer edges, so it selects the shorter path through Dublin

Figure 2: Path selection on the eu-west-1 core network edge

This gives DeepL a per-Region lever. An on-premises AS_PATH prepend that makes one location’s path longer changes the decision only on the core network edge that uses that location.

Why DeepL doesn’t use local preference for the drain: By default, the Direct Connect gateway gives each Region its own preferred locations: the Direct Connect locations associated with that Region. That default is what gives each Region its closest exit, and it applies only while the prefix carries no local preference community. As soon as you tag a prefix, your ranking replaces the default and applies to every Region at once. DeepL advertises the same /16 from both data centers, so lowering the preference on the Dublin advertisement would change the exit for all Regions, not only eu-west-1. The Regions that aren’t being drained would lose their closest exit. A different ranking per Region would require more-specific prefixes per location, which is the per-link configuration DeepL wanted to avoid.

The maintenance drain in practice

To drain the Dublin link, DeepL prepends its prefixes on the Dublin virtual interface from its on-premises routers. This has two effects:

  • With at least two prepends, the path that the eu-west-1 edge receives from the Direct Connect gateway is longer than the paths it learns from the eu-central-1 and eu-north-1 edges. The eu-west-1 edge now prefers a peer path. When two peer edges offer identical routes, AWS Cloud WAN selects one of them. The eu-west-1 traffic then crosses the core network and leaves through either the Copenhagen or the Stockholm Direct Connect location.
  • The eu-central-1 and eu-north-1 edges are untouched. Their local path from the Direct Connect gateway is still the shortest, so closest exit is preserved everywhere except in the Region being drained.

The following diagram shows egress during a drain of the Dublin link.
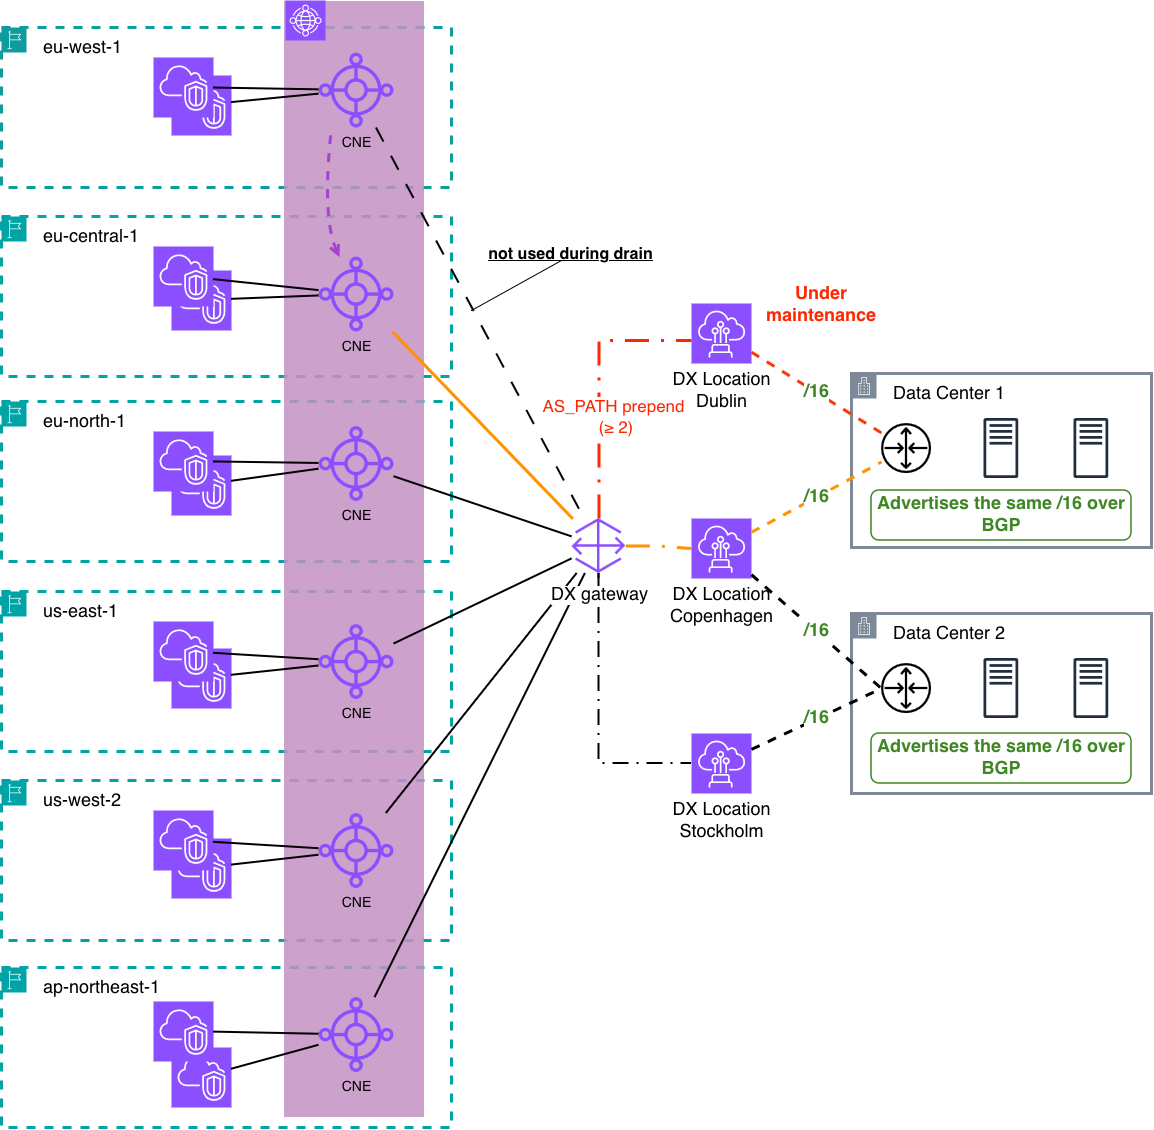
Draining the Dublin Direct Connect link with an AS_PATH prepend. The eu-west-1 edge egresses through Copenhagen (Stockholm is equally possible) while the other European Regions keep their local exit

Figure 3: Draining the Dublin Direct Connect link with an on-premises AS_PATH prepend

All BGP sessions stay up during the drain. The prepend makes the Dublin path less preferred, so traffic moves before the link is taken down. Because no routes are withdrawn, DeepL avoids the convergence gap that a route withdrawal causes. Of the three European edges, only the eu-west-1 edge changes its decision.

Validate each step in a non-production environment first.

  1. Confirm steady state: each Region’s core network edge egresses through its local Direct Connect location.
  2. Apply the on-premises AS_PATH prepend (at least two prepends, and DeepL uses five) to DeepL’s prefixes advertised on the Dublin Direct Connect virtual interface, so that the path the eu-west-1 edge receives from the Direct Connect gateway is longer than the paths it learns from its peer edges.
  3. Lower the BGP local preference on the Dublin sessions on DeepL’s on-premises routers, so that traffic toward AWS also moves to the Copenhagen and Stockholm Direct Connect locations.
  4. Verify that the eu-west-1 edge now selects a path learned from the eu-central-1 or eu-north-1 edge, and confirm that those two edges still egress locally.
  5. Confirm that traffic in both directions has shifted off the Dublin link and is stable.
  6. Perform the physical or router maintenance on the drained Dublin link.
  7. Reverse the change: remove the prepend, restore the local preference on the Dublin sessions, and confirm the eu-west-1 edge returns to its local Dublin path.

Considerations

Plan for the following before you use this pattern:

  • Inter-Region data transfer: While the drain is in place, eu-west-1 traffic crosses Regions on the core network. Plan for inter-Region data transfer charges for the duration of the maintenance window.
  • Prepend count: Use at least two prepends. A single prepend only ties the path length with the peer paths, and on a tie AWS Cloud WAN prefers the route propagated from the Direct Connect gateway, so the drained location would still be used. DeepL uses five prepends for margin.
  • Fallback location: With default path selection, AWS Cloud WAN chooses between equal peer paths, so you don’t control whether Copenhagen or Stockholm takes the displaced traffic. Routing policies, covered in the next section, address this.
  • Traffic toward AWS: The prepend only steers traffic leaving AWS. Traffic from the data centers toward AWS is chosen by DeepL’s own routers. During a drain, DeepL lowers BGP local preference on its routers for routes learned over the Dublin sessions, so this traffic also moves off the drained link, and restores it afterward. This setting only affects DeepL’s own routers. It is separate from the Direct Connect local preference communities described earlier, which DeepL doesn’t use. Because the two directions are chosen independently, traffic can leave AWS through one location and return through another. If a stateful firewall sits in the path, traffic must be symmetric, so make sure both directions use the same fallback location.
  • Regions without a local Direct Connect location: Check egress for Regions that have no local Direct Connect location, such as the US and Tokyo Regions in DeepL’s case, before and during the drain, and confirm that none of them still uses the drained link.

What’s next for DeepL: AWS Cloud WAN routing policies

The maintenance drain uses the default path selection of AWS Cloud WAN and doesn’t need a routing policy. Going forward, DeepL plans to adopt routing policies.

AWS Cloud WAN routing policies are priority-ordered rules that give explicit control over route propagation and BGP path attributes inside the core network. Two use cases are on DeepL’s roadmap:

  • Deterministic maintenance failover: With default path selection, AWS Cloud WAN chooses which remaining location takes the displaced traffic. With a routing policy, DeepL can set an explicit preference, so a drained Region’s traffic lands on a location that DeepL chooses.
  • Route filtering and summarization: As DeepL adds locations, a routing policy can summarize routes in the core network instead of DeepL hand-crafting more-specific routes per link. This keeps the number of advertised routes manageable.

Conclusion

For multi-Region enterprises that rely on default closest-exit egress, it helps to identify where the egress decision is made before changing BGP attributes. With Direct Connect attached natively to AWS Cloud WAN, each core network edge makes that decision based on the preserved on-premises AS_PATH. DeepL uses this to drain a single Direct Connect link with an AS_PATH prepend while every other Region keeps its local exit. As a next step, DeepL plans to use AWS Cloud WAN routing policies to choose the fallback location and to summarize routes.

If you operate multi-Region Direct Connect at scale, review Direct Connect gateway attachments in AWS Cloud WAN, Simplify global hybrid connectivity with AWS Cloud WAN and AWS Direct Connect integration, and Direct Connect routing policies and BGP communities, and validate the drain in a test environment before your next maintenance window.

To learn more about AWS Cloud WAN, visit the AWS Cloud WAN product page.

Acknowledgements

We thank the DeepL networking team for partnering on this post and for sharing their architecture and operational experience with the community.


About the authors

Guzman Freigedo

Guzman Freigedo

Guzman is a Senior Network Engineer at DeepL in Amsterdam, operating the company’s data center, global WAN, and internet edge networks. Guzman led DeepL’s adoption of AWS Cloud WAN and works on automating manual operations across DeepL’s network.

Oliver Geiselhardt-Herms

Oliver Geiselhardt-Herms

Oliver is the Lead Network Architect at DeepL, where he has led the architecture, global expansion, and automation of DeepL’s end-to-end network infrastructure since 2023. He has more than 12 years of experience building and operating large-scale infrastructure at companies including Google and Cloudflare, and holds a Computer Science degree with a specialization in Telecommunications. At DeepL, Oliver leads core routing, global WAN, and hybrid cloud connectivity for the company’s AI platforms.

Toni Gharib

Toni Gharib

Toni is a Technical Account Manager at Amazon Web Services based in Germany, where he partners with enterprise customers on networking, hybrid connectivity, and cloud architecture. He collaborated with the DeepL networking team to document this pattern for Direct Connect maintenance across Regions. Outside of work, Toni enjoys spending time with his son playing football.

Rojda Müller

Rojda Müller

Rojda is a Technical Account Manager in the AWS ISV organization. She partners with SaaS companies across Germany on their AWS environments. She advises on cost optimization, networking, resiliency, and automation, and helps customers design systems that meet their business requirements. Her recent work includes supporting the DeepL networking team on their AWS Cloud WAN adoption.

AWS Week In Review – July 18, 2022

Post Syndicated from Channy Yun original https://aws.amazon.com/blogs/aws/aws-week-in-review-july-18-2022/

Last week, AWS Summit New York was held in person at the Javits Center with thousands of attendees and over 100 sponsors and partners. During the keynote, Martin Beeby, AWS Principal Developer Advocate, talked about how innovations in cloud infrastructure enable customers to adapt to challenges and seize new opportunities. It included Liz Fong-Jones‘s great migration story of AWS Graviton in Honeycomb and Elliott Cordo‘s story of improving pharmacy experiences using AWS analytics and machine learning services in Capsule.

Watch the full keynote video!

A Recap of AWS Summit NY Announcements
During the keynote, we announced the general availability of some new services:

Amazon Redshift Serverless – This serverless option lets you analyze data at any scale without having to manage data warehouse infrastructure. You can now create multiple serverless endpoints per AWS account and Region using namespaces and workgroups and enjoy reducing serverless compute costs compared to the preview. To learn more, check out Danilio’s blog post, this demo video, and the latest episode of The Official AWS Podcast. We also introduced new features of row-level security (RLS), which implement fine-grained access to the rows in tables, and automated materialized view to lower query latency for repeatable workloads.

AWS Cloud WAN – This new network service makes it easy to build and operate wide area networks (WAN) that connect your data centers and branch offices, as well as multiple VPCs in multiple AWS Regions. To learn more, read Seb’s blog post.

Amazon DevOps Guru’s Log Anomaly Detection and Recommendations – This new feature identifies anomalies such as increased latency, error rates, and resource constraints within your app and then sends alerts with a description and actionable recommendations for remediation. To learn more, see Donnie’s blog post as a new News Blog writer.

Last Week’s Launches
Here are some other launches that caught my attention last week:

AWS AppConfig, a feature of AWS Systems Manager, makes it easy for customers to quickly and safely configure, validate, and deploy feature flags and application configuration. Now, we have announced AWS AppConfig Extensions, a new capability that allows customers to enhance and extend the capabilities of feature flags and dynamic runtime configuration data.

Available extensions at launch include AppConfig Notification extensions that push messages about configuration updates to Amazon EventBridge, Amazon SNS, Amazon SQS, or a Jira extension to track Feature Flag changes in AppConfig as Atlassian’s Jira issues. To get started, read Announcing AWS AppConfig Extensions and AppConfig Extensions.

Amazon VPC Flow Logs for Transit Gateway is a new capability that allows customers to gain deeper visibility and insights into network traffic on AWS Transit Gateway. With this feature, Transit Gateway can export detailed information, such as source/destination IPs, ports, protocols, traffic counters, timestamps, and various metadata for all of the network flow traversing through the Transit Gateway. To learn more, read Introducing VPC Flow Logs for AWS Transit Gateway and Logging network traffic using Transit Gateway Flow Logs.

AWS Lambda Powertools for TypeScript is an open-source developer library that can help you incorporate Well-Architected Serverless best practices focusing on three observability features: distributed tracing (Tracer), structured logging (Logger), and asynchronous business and application metrics (Metrics). Powertools is also available in the Python and Java programming languages. To learn more, see the blog post Simplifying serverless best practices with AWS Lambda Powertools for TypeScript. You can submit feedback, ideas, and issues directly on our GitHub project.

AWS re:Post is a vibrant Q&A community that helps you become even more successful on AWS. You can now add a profile picture or avatar to your account and add inline images such as diagrams or screenshots to support your questions or answers. Add your profile picture and start using inline images today!

For a full list of AWS announcements, be sure to keep an eye on the What’s New at AWS page.

Other AWS News
Here are some news, blog posts, and video series for you to know:

In July 2021, we notified users about the end of support for Internet Explorer 11, which is now approaching on July 31, 2022. The browser will no longer be supported in the AWS Management Console, web-based services such as Amazon QuickSight, Amazon Chime, Amazon Honeycode, and some other AWS websites. After that date, we can no longer guarantee that the features and webpages will function properly on IE 11. For more information, please visit AWS Supported Browsers.

In fall 2021, we began offering a free multi-factor authentication (MFA) security key to AWS account owners in the United States. Now eligible customers can order the free MFA security key through the ordering portal in the AWS Management Console. At this time, only U.S.-based AWS account root users who have spent more than $100 each month over the past 3 months are eligible to place an order. For more information, see our Free MFA Security Key page.

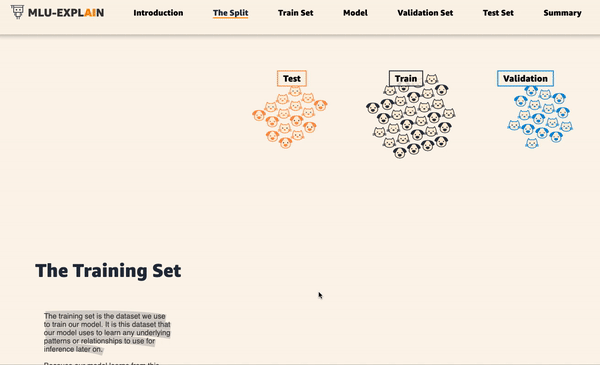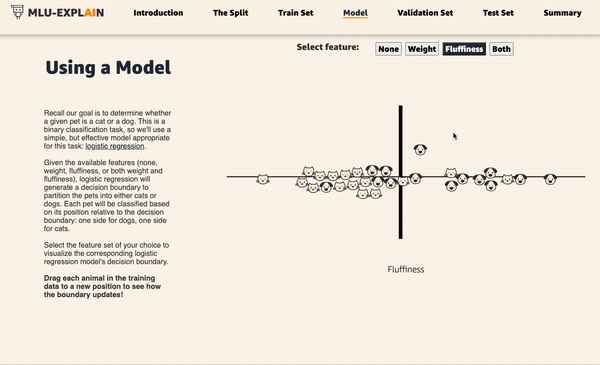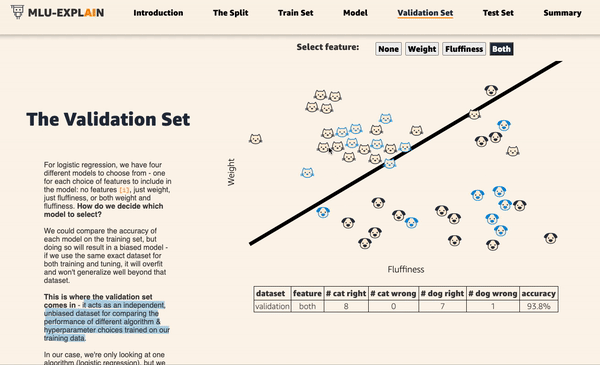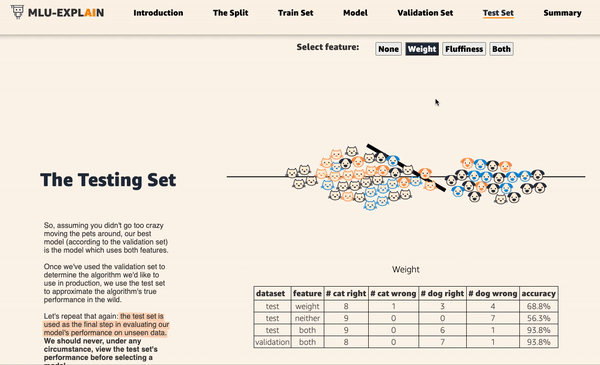
Amazon’s Machine Learning University expands with MLU Explains, a public website containing visual essays that incorporate fun animations and scrollytelling to explain machine learning concepts in an accessible manner. The following animation teaches the concepts of data splitting in machine learning using an example model that attempts to determine whether animals are cats or dogs. To learn more, read the Amazon Science blog post.

This is My Architecture is a video series that showcases innovative architectural solutions on the AWS Cloud by customers and partners. In June and July, over 15 episodes were updated, including GoDaddy, Riot Games, and Hudl. Each episode examines the most interesting and technically creative elements of each cloud architecture.

Upcoming AWS Events in August
Check your calendars and sign up for these AWS events:

AWS SummitRegistration is open for upcoming in-person AWS Summits that might be close to you in August: Sao Paulo (August 3–4), Anaheim (August 18), Taiwan (August 10–11), Chicago (August 28), and Canberra (August 31).
AWS Innovate – Data Edition – On August 23, learn how a modern data strategy can support your present and future use cases, including steps to build an end-to-end data solution to store and access, analyze and visualize, and even predict.

AWS Innovate – For Every Application Edition – On August 25, learn about a wide selection of AWS solutions across compute, storage, networking, hybrid, and edge infrastructure to help you scale application resources seamlessly and optimally.

Although these two Innovate events will be held in Asia Pacific and Japan time zones, you can view on-demand videos for two months following your registration.

If you’re interested in learning modern development practices live in New York City, I recommend joining AWS Solutions Day on August 10. I love advanced topics to focus on building new web apps with Java, JavaScript, TypeScript, and GraphQL.

If you’re interested in learning AWS fundamentals and preparing for AWS Certifications, there are several virtual events in August, such as AWS Cloud Practitioner Essentials Day, AWS Technical Essentials Day, and Exam Readiness for AWS Certificates.

That’s all for this week. Check back next Monday for another Week in Review!

— Channy

This post is part of our Week in Review series. Check back each week for a quick roundup of interesting news and announcements from AWS!

New – Cloud WAN : A Managed WAN Service

Post Syndicated from Sébastien Stormacq original https://aws.amazon.com/blogs/aws/new-cloud-wan-a-managed-wan-service/

I am pleased to announce the availability of AWS Cloud WAN, a new network service that makes it easy to build and operate wide area networks (WAN) that connect your data centers and branch offices, as well as multiple VPCs in multiple AWS Regions.

Typically, large enterprises have resources running in different on-premises data centers, branch offices, and in the cloud. To connect these resources, network teams build and manage their own global networks using multiple networking, security, and internet services from multiple providers. They most probably use several technologies and providers to manage cloud-based networks, to connect their data centers to the AWS cloud, and for the connectivity between on-premises data centers and branch offices. All of these networks take different approaches to connectivity, security, and monitoring, resulting in an intricate patchwork of individual networks that are complicated to configure, secure, and manage.

For example, to prevent unauthorized access to resources running across locations that are connected with different network technologies, network operation teams must piece together different firewall solutions from different vendors and then manually configure and manage the policies between them. Every new location, network appliance, and security requirement exponentially increases complexity.

With Cloud WAN, networking teams connect to AWS through their choice of local network providers, then use a central dashboard and network policies to create a unified network that connects their locations and network types. This eliminates the need to configure and manage different networks individually, even when they are based on different technologies. Cloud WAN generates a complete view of your on-premises and AWS networks to help you visualize the health, security, and performance of your entire network.

Cloud WAN provides advanced security and network isolation, and I am excited by the possibilities offered by this network segmentation. You can use policies in Cloud WAN to easily segment your network traffic regardless of how many AWS Regions or on-premises locations you add to your network. For example, you can easily isolate network traffic from retail payment processing from other traffic on your corporate network while still giving both segments access to shared corporate resources. Another example would be the isolation of your development and production environment by creating logical network segments for each environment. This makes it easier to ensure consistent security policies when connecting large numbers of locations with your VPCs especially when your policies need to apply to large groups with unique security and routing requirements. Cloud WAN maintains a consistent configuration across Regions on your behalf. In a traditional network, a segment is like a globally consistent virtual routing and forwarding (VRF) table or a layer 3 IP VPN over an MPLS network. Segments are optional; smaller organizations may use Cloud WAN with one single network segment, encompassing all your traffic.

In addition to network segmentation and the simplicity it brings to your network management tasks, I see four principal benefits of using Cloud WAN:

Centralized management and network monitoring dashboard – Network Manager provides a central dashboard for connecting and managing your branch offices, data centers, VPN connections, and Software-Defined WAN (SD-WAN), as well as your Amazon VPC and AWS Transit Gateway. This dashboard helps you monitor and view the health of your network in one place, simplifying day-to-day operations.

Centralized policy management – You define access controls and traffic routing rules in a central network policy document, expressed in JSON. When you update a policy, Cloud WAN uses a two-step process to ensure accidental errors do not affect your global network. First, you review and validate that your changes will work as expected in production. Once you approve the changes, Cloud WAN handles the configuration details for the entire network. You can change your policy document using the AWS Management Console or Cloud WAN APIs.

Multi-Region VPC connectivity – Cloud WAN connects your VPCs across AWS Regions. Using a simple network policy document, you can create global networks that connect all of your EC2 resources, or you can choose to segment them across Regions.

Built-in automation. Cloud WAN can automatically attach new VPCs and network connections to your network, so you do not need to approve each change manually. It reduces the operational overhead involved in managing a growing network. You do this by tagging attachments and defining network policies that automatically map attachments with a certain tag to a specific network segment. With this tagging structure in place, you can choose which attachments can join a segment automatically, which segments require manual approval, and if attachments on the same segment can talk to each other, all based on the tags you choose.

Let’s get started
To get started with Cloud WAN, I open the AWS Management Console. In the VPC section, there is a new entry for AWS Cloud WAN on the menu on the left. Creating and configuring a global network is a four-step process.

First, I start by creating a global network and a core network.

Cloud WAN create global networkAfter entering the Name and an optional Description, I select Next.

Cloud WAN create core networkAfter giving the core network a Name and a Description, I enter my ASN range and the list of Edge locations, and I enter a Segment name and Segment description for my default segment. The default segment is automatically enabled in all selected edge locations.

Second, I define and attach my core networking policy. The core policy defines the rule to control network access across segments and AWS Regions. Third, I configure segments and segment actions. I can see all routes and filter by network Segment and Edge location.

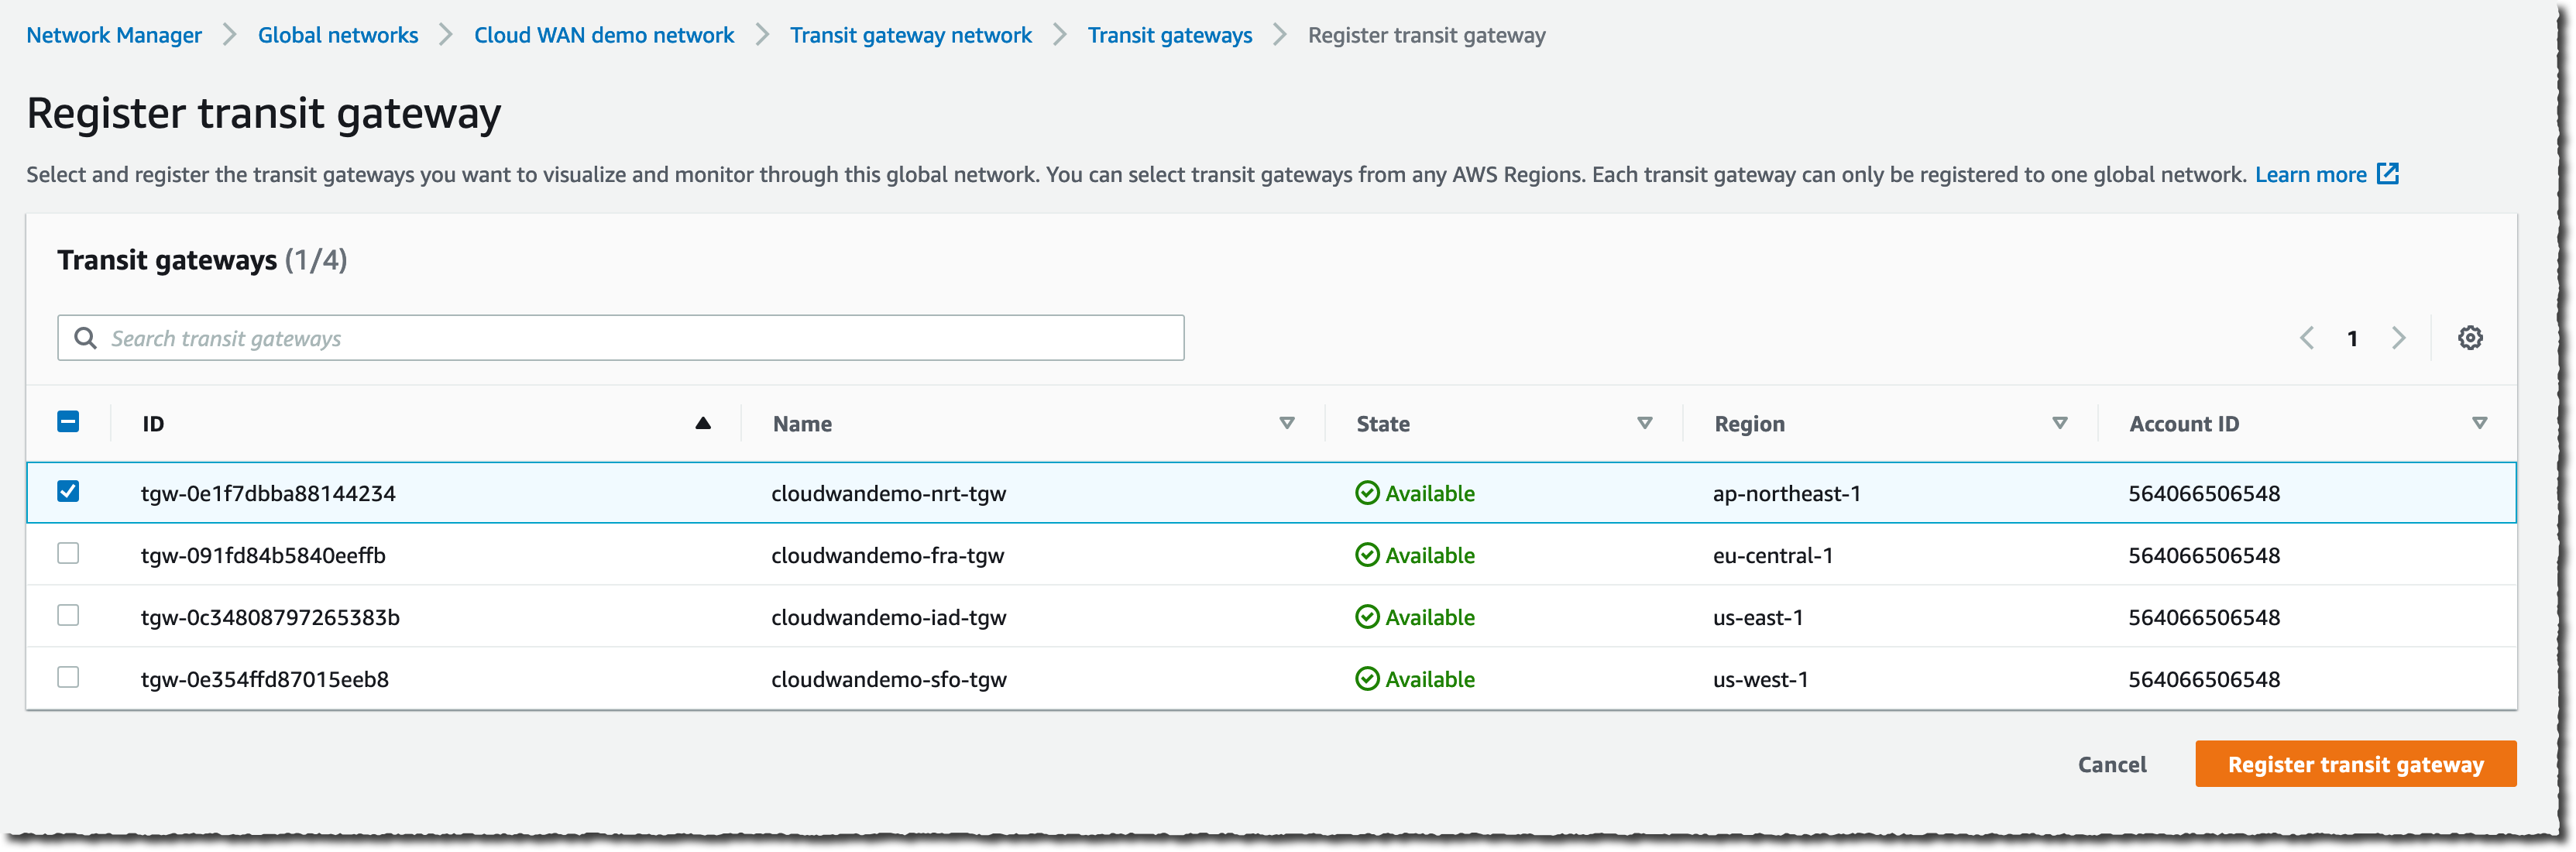
Cloud Wan - RoutesAnd finally, I register the existing Transit Gateway to the new global network.

Cloud WAN - register transit gateways

Once configured, you have a single monitoring dashboard for your global network. You have access to the network inventory.

Cloud Wan - Monitoring inventoryOr you can have more granular and detailed views with Topology graph and Topology tree.

Cloud Wan - Monitoring topology

Other considerations
During the preview period we ran for Cloud WAN, we often received the question: “When should I build networks with Cloud WAN versus Transit Gateway?” This is a valid question because both Transit Gateway and Cloud WAN allow centralized connectivity between Amazon VPC and on-premises locations. Transit Gateway is a Regional network connectivity hub and is optimal when you operate in a few AWS Regions or when you want to manage your own peering and routing configuration or prefer to use your own automation.

On the other side, Cloud WAN is a managed wide area network (WAN) that unifies your data center, branches, and AWS networks. While you can create your own global network by interconnecting multiple Transit Gateways across Regions, Cloud WAN provides built-in automation, segmentation, and configuration management features designed specifically for building and operating global networks. Cloud WAN has added features such as automated VPC attachments, integrated performance monitoring, and centralized configuration.

But the world is better together, you can peer your Transit Gateways with Cloud WAN’s Core Network Edges (CNEs) and benefit from the central management and monitoring capabilities I described earlier. The peering between Cloud WAN and Transit Gateway keeps your options open – you can migrate from one to another, or use Cloud WAN to centrally connect all your existing Transit Gateways.

But then, AWS released SiteLink in December last year. When should you use SiteLink, and when should you use AWS Cloud WAN? Depending on your use case, you might choose one, the other, or both. Cloud WAN can create and manage networks of VPCs across multiple Regions. SiteLink, on the other hand, connects Direct Connect locations together, bypassing AWS Regions to improve performance. Direct Connect is one of the several connectivity options that you will be able to natively use with Cloud WAN in the future. As of today, you interconnect Direct Connect with Cloud WAN via Transit Gateway peering connections.

Availability and Pricing
Cloud WAN is available today in US East (N. Virginia), US East (Ohio), US West (N. California), US West (Oregon), Africa (Cape Town), Asia Pacific (Mumbai), Asia Pacific (Singapore), Asia Pacific (Sydney), Asia Pacific (Tokyo), Canada (Central), Europe (Frankfurt), Europe (Ireland), Europe (London), Europe (Milan), Europe (Paris), Europe (Stockholm), and Middle East (Bahrain) AWS Regions.

As usual, there are no setup or upfront fees, and billing is on-demand based on your actual usage. There are four factors that determine what you pay for using AWS Cloud WAN. First, the number of Core Network Edges (CNEs) deployed. Second, the number of attachments to each CNE. An attachment might be an Amazon VPC, a VPN, or an SD-WAN. Third, the number of Transit Gateways peered with your CNEs. And fourth, there is a data processing charge for traffic sent through each CNE.

On top of these factors that are specific to Cloud WAN, sending data between Regions triggers an EC2 inter-Region data transfer out charge. While EC2 inter-Region data transfer out is billed separately from Cloud WAN, it’s a factor in the total cost of the Cloud WAN service. The pricing page has the details.

Go build your global network!

— seb