Tag Archives: Events

Rapid7 at Black Hat USA 2026: See preemptive security in action

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/dr-black-hat-usa-2026-preemptive-security-in-action

Black Hat USA returns to Mandalay Bay in Las Vegas this August, bringing together security practitioners, researchers, and leaders from around the world. Rapid7 will be there in the Business Hall, with new capabilities, live demonstrations, expert-led sessions, and two days of activities at the Border Grill.

This year, our focus is preemptive security: helping security teams anticipate credible risk, respond at machine speed, and maintain an accurate view of their security and compliance posture as their environment changes.

Visit the Rapid7 booth at Black Hat USA

You can find Rapid7 at booth #2445 in the Mandalay Bay Business Hall, open and running on the following days and times:

  • Tuesday, August 4: 4:00–7:00 p.m.

  • Wednesday, August 5: 9:00 a.m.–6:00 p.m.

  • Thursday, August 6: 9:00 a.m.–4:00 p.m.

The booth will include two demonstration stations, seating, giveaways, and our friendly team of Rapid7 experts – there to help you explore the challenges most relevant to your organization. A chess-inspired theme reflects the principle behind preemptive security: understanding what may happen next and acting before risk becomes an incident.

Live demonstrations will cover four connected areas of the Rapid7 platform:

Predictive risk and vulnerability management: See how attacker behavior and exposure context can help teams focus remediation on vulnerabilities that present credible risk.

Agentic threat detection and response: Explore how the Rapid7 AI Engine and technology from Kenzo Security support adaptive investigations and reduce the time analysts spend gathering context.

Continuous compliance automation: See how Cyber GRC connects governance workflows with live security data, automates evidence collection, and identifies control drift.

Preemptive MDR: Learn how continuous SOC operations, exposure context, and Rapid7 Labs threat intelligence can extend the coverage of internal security teams.

Explore the latest Rapid7 launches at Black Hat

Black Hat will provide a closer look at several additions to the Rapid7 platform, including the general availability of Cyber GRC.

Cyber GRC brings security operations and governance teams closer together by connecting GRC workflows with live security data. The solution draws evidence from SecOps telemetry into compliance dashboards, helping teams maintain a current view of their controls, while AI-assisted workflows reduce the manual inputs involved in third-party risk questionnaires and other repetitive tasks.

Attendees can also learn more about Preemptive MDR Alerts, predictive vulnerability management, and enhanced agentic SOC investigations. These capabilities combine exposure data, asset criticality, threat intelligence, and detection context to help teams identify where attackers are most likely to act. Some will be presented as early-access previews, so availability will vary.

Join us at Border Grill

Rapid7 will take over the Border Grill at Mandalay Bay on Wednesday, August 5 and Thursday, August 6. The space will include additional demonstrations, meeting areas, expert presentations, breakfasts & lunches, and opportunities to speak with Rapid7 leaders and product teams.

Highlights from the agenda include:

Preemptive Security for the Age of AI

Wednesday, August 5, 12:00–12:45 p.m.

Rapid7 Executive Chairman Corey Thomas will discuss how AI-driven threats are changing security operations and what it takes to move toward a more preemptive model.

Agentic SOC: Threat Detection and Response

Thursday, August 6, 9:30–10:15 a.m.

Lisa Washburn, Senior Director of Product Management, will explore how AI agents can investigate alerts at machine speed while keeping expert judgment involved.

Cyber GRC in the Age of AI

Thursday, August 6, 11:30 a.m.–12:15 p.m.

Jon Schipp, Senior Director of Product Management, will show how live security data and automated evidence can support continuous audit readiness.

Border Grill will also host live demos, customer and executive meetings, and the Rapid7 Happy Hour on Wednesday. VIP access begins at 4:00 p.m., followed by general admission from 5:00–7:30 p.m.

Hear from Rapid7 security researchers

Rapid7 researchers Jack Heysel and Spencer McIntyre will present The Metasploit Framework 6.5: Malleable C2 Payloads, New Relay Capability and Protocol Session Upgrades at Arsenal Station 4 in the Business Hall on Wednesday, August 5 from 4:00–5:00 p.m.

Book time with Rapid7 at Black Hat

Whether your priority is reducing exposure, giving SOC analysts better context, improving response speed, or strengthening audit readiness, you can book a meeting or tailored demonstration with the Rapid7 team.

Visit us at booth #2445, join us at Border Grill, or reserve time in advance. Register for the Rapid7 Black Hat experience here.

Enterprise security at machine speed: AWS Black Hat 2026 preview

Post Syndicated from Rahul Sahni original https://aws.amazon.com/blogs/security/enterprise-security-at-machine-speed-aws-black-hat-2026-preview/

Black Hat 2026 (Aug 1-6, 2026) brings together over 22,000 security practitioners, researchers, and CISOs who build, break, and defend enterprise infrastructure. They’re security professionals who push the limits of offensive and defensive security and demand proof over promises. As frontier security models like Mythos reshape the enterprise landscape, they need security that operates at the same speed as the events they face. This August, Amazon Web Services (AWS) returns to Las Vegas to meet with our customers and partners to show how we’re delivering enterprise security at machine speed.

At Black Hat USA 2026, connect with AWS through live demos, a practitioner session on autonomous security operations, and an executive roundtable on building durable AI security architectures, plus networking receptions with customers and partners. Here’s where to find us and what you’ll take away.

Experience AWS security innovation in action

Visit us at Booth #1648 to explore five interactive demo pedestals, each aligned to a pillar of our AI-powered security story:

  • Post-Mythos enterprise security: AWS uses multiple frontier AI reasoning models to find issues, validate exploitability, and autonomously fix exposures, compressing mean-time-to-remediation from days to minutes. Learn how AWS Continuum helps you find risks before you ship, prioritize by real business impact, and remediate at machine speed while you stay in control.
  • AI-powered investigations: Amazon GuardDuty AI-powered investigations automatically analyze findings and the accounts around them to separate true threats from benign activity at scale. Drawing on log activity, resource configuration, internet reachability, and historical findings, it delivers triage reports that match expert-level accuracy, freeing your team to focus on what matters.
  • Purpose-built AI workload security: AWS extends the enterprise security controls you already trust to address the unique demands of AI workloads. Amazon Bedrock helps you build and deploy generative AI applications, with hundreds of top foundation models plus built-in safety controls, guardrails, and evaluation tools. Amazon Bedrock AgentCore Identity keeps you in full control of what your AI agents can access.
  • Full-stack multicloud security: AWS Security Hub Extended delivers full-stack security by integrating AWS services with 21 curated partner solutions across nine categories, from endpoint and identity to AI, with pay-as-you-go pricing, one console, and one bill. All findings flow in OCSF format with zero integration work, and a risk correlation engine traces paths across multicloud so your team fixes root causes rather than chasing symptoms.
  • AWS Partner solutions: A dedicated partner demo pedestal runs live demonstrations from select AWS Partners, showing how their solutions integrate with AWS to address your most critical security challenges. With over 25 partners rotating throughout Business Hall hours, you get a firsthand view of how these integrations work together to strengthen your security posture.

Theater sessions: Want to go deeper on a specific topic without committing to a full session? During expo hours, our theater hosts 15-minute AWS and partner talks curated around the challenges enterprise security teams face today. Topics range from enabling AI adoption securely, to unifying visibility across clouds, to automating response. Subject matter experts from AWS and our partners lead each session and give you insights you can bring back to your team. Featured sessions include:

  • From finding to fix at machine speed with AWS Continuum
  • Securing the agentic AI stack
  • Architecting defense-in-depth for AI workloads
  • Network security strategies for the post-Mythos era
  • One console for unified full-stack security

For the latest theater session schedule, including dates and times, visit AWS at Black Hat 2026.

Engagement Zone: Take a quick break and test your detection skills in a gamified, hands-on challenge. Race the clock to resolve security issues and collect power-ups that speed your mission to secure the environment. Rack up your score, lock in your percentile rank, and see how you stack up against every other player.

Beyond the booth: Sessions and executive roundtable

AWS security experts share insights at speaking sessions and host an executive roundtable at Black Hat USA 2026.

Speaking Session | Machine-Speed Defense: Building an Autonomous Security Operations Loop for the AI Era
Wednesday, August 5, 10:15–10:35 AM PDT
Pulse Stage 2
In a post-Mythos world, organizations need to use AI-powered reasoning to discover, correlate, validate, and remediate security exposures at machine speed. This session provides a blueprint for building an autonomous security operations loop, using business-context graphs and sandbox validation, to unlock machine-speed defense as a durable competitive edge.

Executive Roundtable | Autonomous Defense at Cloud Scale: Critical Choices for Security Leaders Today
Wednesday, August 5, 11:00 AM–12:00 PM PDT
Breakers F
As agentic AI and frontier models reshape the threat landscape, foundational security remains essential, and organizations that layer autonomous workload governance on top can turn AI into a true security force multiplier. This executive roundtable explores how to build a durable, adaptive security harness that accounts for the real economics of AI-powered defense and evolves alongside rapidly advancing models and techniques.

Briefing | ThreatForest: Automated Attack Trees from Source Code
Thursday, August 6, 2:35–3:15 PM PDT
Jasmine, Level 3
Threat modeling is critical, but manual processes can’t keep pace with cloud-focused architectures. This briefing will dive into how ThreatForest uses six specialized AI agents to automatically analyze source code and produce validated attack trees mapped to MITRE ATT&CK with actionable mitigations. Attendees walk away with the open source tool and a reusable multi-agent architecture pattern.

AWS activities and events

Beyond the expo floor, AWS hosts a portfolio of ancillary events built for focused conversations and networking across the security community. Join us at:

Security LIVE! broadcast

Catch Security LIVE! on-site at Mandalay Bay on Wednesday, August 5 and Thursday, August 6. This infotainment-style broadcast brings AWS and AWS Partners together to solve real security challenges for customers across 20-minute conversational segments, covering everything from data protection and compliance to application and perimeter security. With over 30 segments, Security LIVE! showcases the breadth of the AWS security partner ecosystem. Stop by the set to watch it unfold live.

Join us in Las Vegas

Whether you’re exploring how to secure AI workloads, adopting autonomous remediation as frontier models like Mythos reshape the landscape, or unifying security across domains and clouds, the AWS team at Black Hat USA 2026 is ready to help.

Learn more about AWS Security solutions at AWS Cloud Security.

See you in Las Vegas, August 3–6, 2026.


Rahul Sahni

Rahul Sahni

Rahul is a Senior Product Marketing Manager at AWS Security. An avid Amazonian, he embodies the company’s Leadership Principle of Learn and Be Curious in both his professional and personal life, whether diving into emerging security topics or experimenting with new dishes from around the world.

Security Teams Are Ready To Become More Preemptive. What’s Holding Them Back?

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/dr-teams-ready-for-preemptive-security-mdr-survey

The shift toward preemptive security is underway, but most organizations are still navigating the realities of limited resources, fragmented tools, and emerging AI risk. At Rapid7’s recent Global Security Summit, we surveyed attendees to better understand where security leaders and practitioners stand today, what is shaping their priorities, and what they need to move forward. Their responses offer a candid view into the current state of security operations: ambitious, increasingly AI-aware, and ready for change, but still working through the practical challenges of getting there.

For many teams, the direction is clear: security needs to become more proactive, more connected, and more resilient. Attackers are moving quickly, environments are expanding, and teams are under pressure to reduce risk before it turns into business disruption. But the survey results show that most organizations are still somewhere in the middle of that journey.

Where organizations are today

One of the clearest findings is that security operations are increasingly collaborative. According to the survey, 57% of respondents operate in a hybrid internal and MDR model. That reflects a reality many teams know well: internal expertise remains essential, but external support can help extend coverage, add specialist knowledge, and support faster response when internal resources are stretched.

This hybrid model also speaks to the complexity security teams are managing. Modern environments span cloud, identity, endpoints, applications, third parties, and expanding attack surfaces. Keeping watch across all of it requires more than tooling alone. It requires the right mix of people, process, visibility, and support.

At the same time, many organizations are still working to connect the dots across their security ecosystem. Two-thirds of respondents said their security capabilities are only partially integrated. For analysts, partial integration often means more manual work: switching between tools, stitching together context, and making decisions with an incomplete picture. When teams are jumping between systems, manually stitching together context, or working from incomplete data, it becomes harder to act at the speed modern threats demand.

The survey also showed that only 10% of respondents describe their organization as “highly proactive” in predicting and preventing threats, which points to the reality of where many teams are today. The ambition is there, but becoming truly preemptive takes time, integration, and operational maturity. Most organizations are still balancing the day-to-day demands of reactive response with the longer-term work of building a more proactive security model.

Confidence levels tell a similar story. 59% of respondents said they are only somewhat confident in their organization’s ability to prevent attacks before impact. Security teams understand what is at stake, but many still lack full confidence that they can consistently stop threats before they affect the business.

AI is a priority, but trust matters

AI was, of course, another major theme in the survey. Interest is high, especially when it comes to improving efficiency, accelerating triage, and helping teams manage growing volumes of data and alerts, but adoption is still developing. 52% of respondents said AI is in early-stage exploration within their security operations.

AI has clear potential in the SOC and across security operations, from summarizing investigations to enriching alerts, supporting prioritization, and helping analysts move faster. But security teams have to be deliberate about how they apply it. In high-pressure environments where accuracy, context, and accountability matter, AI needs to earn trust.

The survey results show that trust is still a key consideration. 57% of respondents cited securing AI usage as a top AI and security concern, while 44% cited lack of transparency or trust. These responses reflect a practical mindset. Security leaders are thinking about both sides of AI: how it can help defenders move faster, and how to manage the new risks it introduces. Internally, for AI to become operationally valuable, it has to fit into existing workflows, provide explainable outputs, and support human expertise.

What security teams want next

When respondents were asked what is preventing them from becoming more proactive, the top challenges were practical and familiar. 54% cited limited staff or expertise, making capacity one of the biggest barriers to progress. Teams may have the ambition to become more preemptive, but many are already balancing daily alert queues, incident response, vulnerability backlogs, compliance pressure, and business-as-usual security demands.

Visibility is another major factor. 31% of respondents cited lack of visibility across the environment as a barrier to becoming more proactive. Without a clear view of assets, identities, exposures, and attacker activity, teams struggle to prioritize what matters most. This is especially important as organizations look to move from broad detection toward more risk-aware, preemptive action.

The priorities respondents selected show where they want to go next. 41% selected preemptive security as a top security leadership priority, while improving resilience, strengthening incident response, reducing complexity, and improving risk visibility also appeared as recurring themes.

The findings from our Global Security Summit make one thing clear: security teams are ready to move toward more proactive, integrated, and AI-enabled operations, but they need the right visibility, expertise, and confidence to do it well.

To hear more from the experts and practitioners who joined us at the summit, catch up on the on-demand sessions. And to learn how Rapid7 is helping organizations move toward preemptive security, explore Rapid7 Managed Detection and Response, built to disrupt attackers earlier with broad ecosystem coverage, risk visibility, expert guidance, and an AI-powered SOC.

5 Myths About AI in the SOC Security Teams Need to Rethink

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/ai-rethinking-5-soc-myths

AI is now part of almost every conversation in security operations. Most teams are already investing in it, experimenting with it, or trying to understand where it fits. The challenge is not whether to adopt AI, but how to apply it in a way that actually improves outcomes.

At the Rapid7 Global Cybersecurity Summit, the session The AI Dilemma: Automating Defense Without Surrendering Judgment explores how AI is being used in the SOC today, and where it creates real value in practice.

The discussion centers on a set of assumptions that often shape how teams approach AI, and why those assumptions do not always hold up in real environments.

Myth 1: AI will replace analysts

Across the session, there is a consistent focus on how AI supports investigation workflows by reducing repetitive work and surfacing relevant context, allowing analysts to focus on decisions that require judgment. AI helps teams move faster, but responsibility and accountability still sit with people. TL;DR, the role of the analyst is evolving, but it is not disappearing.

Myth 2: More automation means better security outcomes

Automation is valuable when it is applied in the right places. In practice, teams are finding the most benefit in areas such as enrichment, summarization, and triage, where large volumes of data need to be processed quickly. High-impact actions such as containment or configuration changes still require oversight, particularly when they can affect production systems or business operations.

Myth 3: Speed is more important than transparency

As adoption increases, trust becomes more important and analysts need to understand how a conclusion was reached before they act on it, especially in high-pressure situations. The session highlights how explainability builds confidence over time, allowing teams to rely on AI outputs without losing control of the decision-making process.

Myth 4: AI is only about efficiency gains

Efficiency is part of the story, but the impact runs deeper. AI helps connect signals across fragmented environments, reduces cognitive load, and supports more consistent decision-making. It also changes how teams approach investigation by making it easier to surface patterns and identify relationships that would be difficult to see manually.

Myth 5: Attackers benefit more from AI than defenders

Both attackers and defenders are learning how to use AI, and both are moving quickly. What matters for security teams is how they apply it within their own workflows. The session explores how AI strengthens detection, investigation, and response when it is integrated into existing processes rather than treated as a standalone capability.

Where AI creates real value in the SOC

Across the discussion, a clear pattern emerges. AI delivers the most value when it is applied to high-volume, context-heavy tasks, where it can process data, highlight signals, and recommend next steps. Analysts remain central to interpreting those signals, understanding intent, and deciding how to respond.

This balance between automation and oversight is what allows teams to scale their operations without losing confidence in their decisions. It also reflects how AI is being adopted across the industry, with most organizations maintaining moderate to high levels of human involvement as they build trust in these systems.

For SOC leaders, practitioners, and teams exploring AI, the session offers a grounded view of how these technologies are being applied today, and how that approach is continuing to evolve.

Watch the full session to explore how transparent AI supports better decisions in the SOC and how teams are applying it in practice.

Why Security Teams Need To Start Earlier

Post Syndicated from Tom Caiazza original https://www.rapid7.com/blog/post/it-why-security-teams-need-to-start-earlier

Security leaders are facing an unusual set of circumstances. The drumbeat for better security prioritization has been rising for years in boardrooms around the world. The desire is there, but the processes of the past aren’t meeting the needs of the new moment we find ourselves in. 

That gap is not a technology problem. It’s an operating model problem.

At the opening keynote of Rapid7’s 2026 Global Cybersecurity Summit, Craig Adams, Chief Product Officer, Rapid7, Brian Castagna, CSO, Rapid7 and IDC’s Research VP, Craig Robinson framed a simple idea: cyber defense needs to start earlier.

For more on this, download our new ebook, Preemptive Security: From Resilience to Action.

Complexity is outpacing control

Security environments have never been more connected or more difficult to manage. Cloud adoption, SaaS sprawl, third-party dependencies, and identity growth have expanded the attack surface in ways most programs were not designed to handle. Many teams have responded by adding more tools and more telemetry. This has resulted in more fragmentation, more dashboards, and more opportunities for important information to slip through the cracks. 

Teams are spending more time stitching context together than they are effectively reducing risk. This shows up in daily operations with analysts moving between multiple systems to validate alerts, and leaders lacking the clear picture to explain risk to the business. In a time when exposure management and detection & response can live on one platform, that level of fragmentation makes no sense.

Reactive security creates operational drag

The traditional model still dominates most security programs. It goes like this (stop us if you’ve heard this before): 1) Detect an alert. 2) Investigate. 3) Contain. 4) Recover. 5) Repeat, forever. 

Sounds simple, right? And it worked great when environments were simpler and attackers moved slower. That is no longer the case.

Today, initial access often happens quietly through identity abuse or misconfiguration. Attack paths form before an alert even fires. By the time a signal reaches the security team, attackers may already be moving laterally or accessing sensitive systems. This creates a cycle of constant response without consistent risk reduction. Teams get better at handling incidents but struggle to remove the conditions that enable them.

Security operations centers can receive thousands of alerts per day, many of which are low value or false positives. This leaves analysts spending hours triaging signals instead of focusing on the exposures most likely to lead to impact.

More alerts do not make you safer. They create drag. Better context creates better outcomes. 

The issue is prioritization, not visibility

Most organizations are not lacking data. They are lacking the clarity needed to understand the data they have and contextualize it as it relates to their business. Telemetry alone does not answer the question that matters most: what should we do first?

Attackers look for the most effective path into an environment, often combining smaller weaknesses across assets, identities, and systems until they create meaningful access. Security teams need a similarly connected view, one that helps them understand which exposures are exploitable, which assets are most critical, and how those risks relate across the environment. When teams can see that full picture, they can focus remediation on the issues most likely to be used in a real attack, making risk reduction more targeted, efficient, and defensible. 

The result is effort without impact.

Why security needs to start earlier

The summit’s keynote message is direct: meaningful action must move earlier in the lifecycle.

Preemptive Security introduces an operating model designed for that shift. It connects four core elements:

  • Exposure management to identify and prioritize risk

  • Managed detection and response (MDR) to monitor and act

  • Artificial intelligence to reduce noise and accelerate analysis

  • Human expertise to validate and decide

Together, these capabilities create a system that acts before risk becomes impact. Instead of waiting for alerts, teams identify likely breach paths. Instead of reacting to incidents, they reduce exposure ahead of time. Instead of managing disconnected tools, they operate with shared context and clear priorities. Detection and response becomes one leg of the stool with exposure management taking the lead in reducing risk before it becomes an emergency. 

What changes for security leaders

For CISOs and security leaders, this shift means designing programs around likely attack paths, not isolated findings. It means prioritizing investments based on risk reduction, not tool coverage and enabling teams to act decisively without increasing headcount or complexity.

It also changes how success is measured. The goal is fewer surprises, faster containment and reduced exposure before exploitation. It means starting earlier, to increase the likelihood of success. These are outcomes the business understands.

A new starting point for security

Ultimately, the environment has changed faster than the operating model. So the operating model needs to change. Luckily, there’s a proven path forward that can prevent the attacks from bad actors already moving in earlier, using technology to scale their operations, and exploiting small weaknesses to get a foothold. 

Preemptive Security provides the framework to close that gap. It helps teams reduce noise, focus on what matters, and act with confidence before disruption occurs. Security does not start with an alert. It starts with understanding risk early enough to do something about it.

Watch the keynote on demand or download the eBook, Preemptive Security: From Resilience to Action, to explore the model in more detail.

Introducing Amazon Bedrock Managed Knowledge Base for faster, more accurate enterprise AI applications

Post Syndicated from Daniel Abib original https://aws.amazon.com/blogs/aws/introducing-amazon-bedrock-managed-knowledge-base-for-faster-more-accurate-enterprise-ai-applications/

Today, we’re announcing Amazon Bedrock Managed Knowledge Base, a new set of capabilities that enables developers to build enterprise-grade generative AI applications with their proprietary data in minutes. Organizations building agentic AI applications need secure, reliable, and up-to-date access to enterprise-wide data to deliver accurate, fast, and trusted outcomes. Managed Knowledge Base abstracts away the complexity of building and managing retrieval-augmented generation (RAG) pipelines, allowing developers to focus on business outcomes rather than infrastructure management.

Developers building knowledge bases for their agents face three key challenges today:

  • Connecting to enterprise data – Enterprise knowledge lives across disparate systems with different content types, access control lists, and document formats. Building and maintaining custom connectors for each source adds complexity that slows down development.
  • Optimizing RAG accuracy – Best practices for retrieval-augmented generation keep evolving. Developers need to experiment with different parsing strategies, chunking approaches, embedding models, and agentic retrieval behaviors to get accurate answers from their data.
  • Managing infrastructure at scale – Organizations need to serve large knowledge bases with millions of documents, or manage thousands of smaller knowledge bases across teams. Both patterns require reliable infrastructure, security enforcement, and cost control.

These challenges require developers to repeatedly perform undifferentiated work instead of focusing on their applications.

Amazon Bedrock Managed Knowledge Base addresses these challenges by abstracting away the multiple infrastructure components developers traditionally have to assemble and maintain themselves (storage, retrieval, embeddings, re-ranking, and foundation model selection) into a single managed primitive. By default, the service automatically selects and manages a default embeddings model, re-ranker model, and foundational model on your behalf, so you can get up to speed quickly without needing to pick or maintain one yourself. On top of this managed foundation, three core innovations further improve ease of use and accuracy:

  • Native data connectors – Six pre-built ingestion connectors that natively pull enterprise data and permissions from SaaS applications, eliminating the overhead developers face in managing application-specific requirements. At launch, we support Amazon S3, SharePoint, Confluence, Web Crawler, Google Drive, and OneDrive.
  • Smart Parsing – Different content types and sources require different approaches to achieve accurate retrieval. Smart Parsing handles this complexity automatically, selecting the right parsing strategy for each data type and connector to provide the highest accuracy for your agents.
  • Agentic Retriever – Optimized for complex queries that require multiturn, multihop retrieval within a single knowledge base or across multiple knowledge bases. Agentic Retriever automatically infers end-user intent and draws relevant context from institutional knowledge spread across data sources and modalities.

With just a few lines of code, Amazon Bedrock Managed Knowledge Base automatically manages and scales the end-to-end RAG pipeline that powers your enterprise knowledge agents. For agent builders, it’s available as a pre-built target type in Amazon Bedrock AgentCore Gateway, reducing integration to a few lines of code, auto-generating role-based permissions, and providing observability and evaluation metrics in the AgentCore Observability dashboard.

Getting started with Amazon Bedrock Managed Knowledge Base
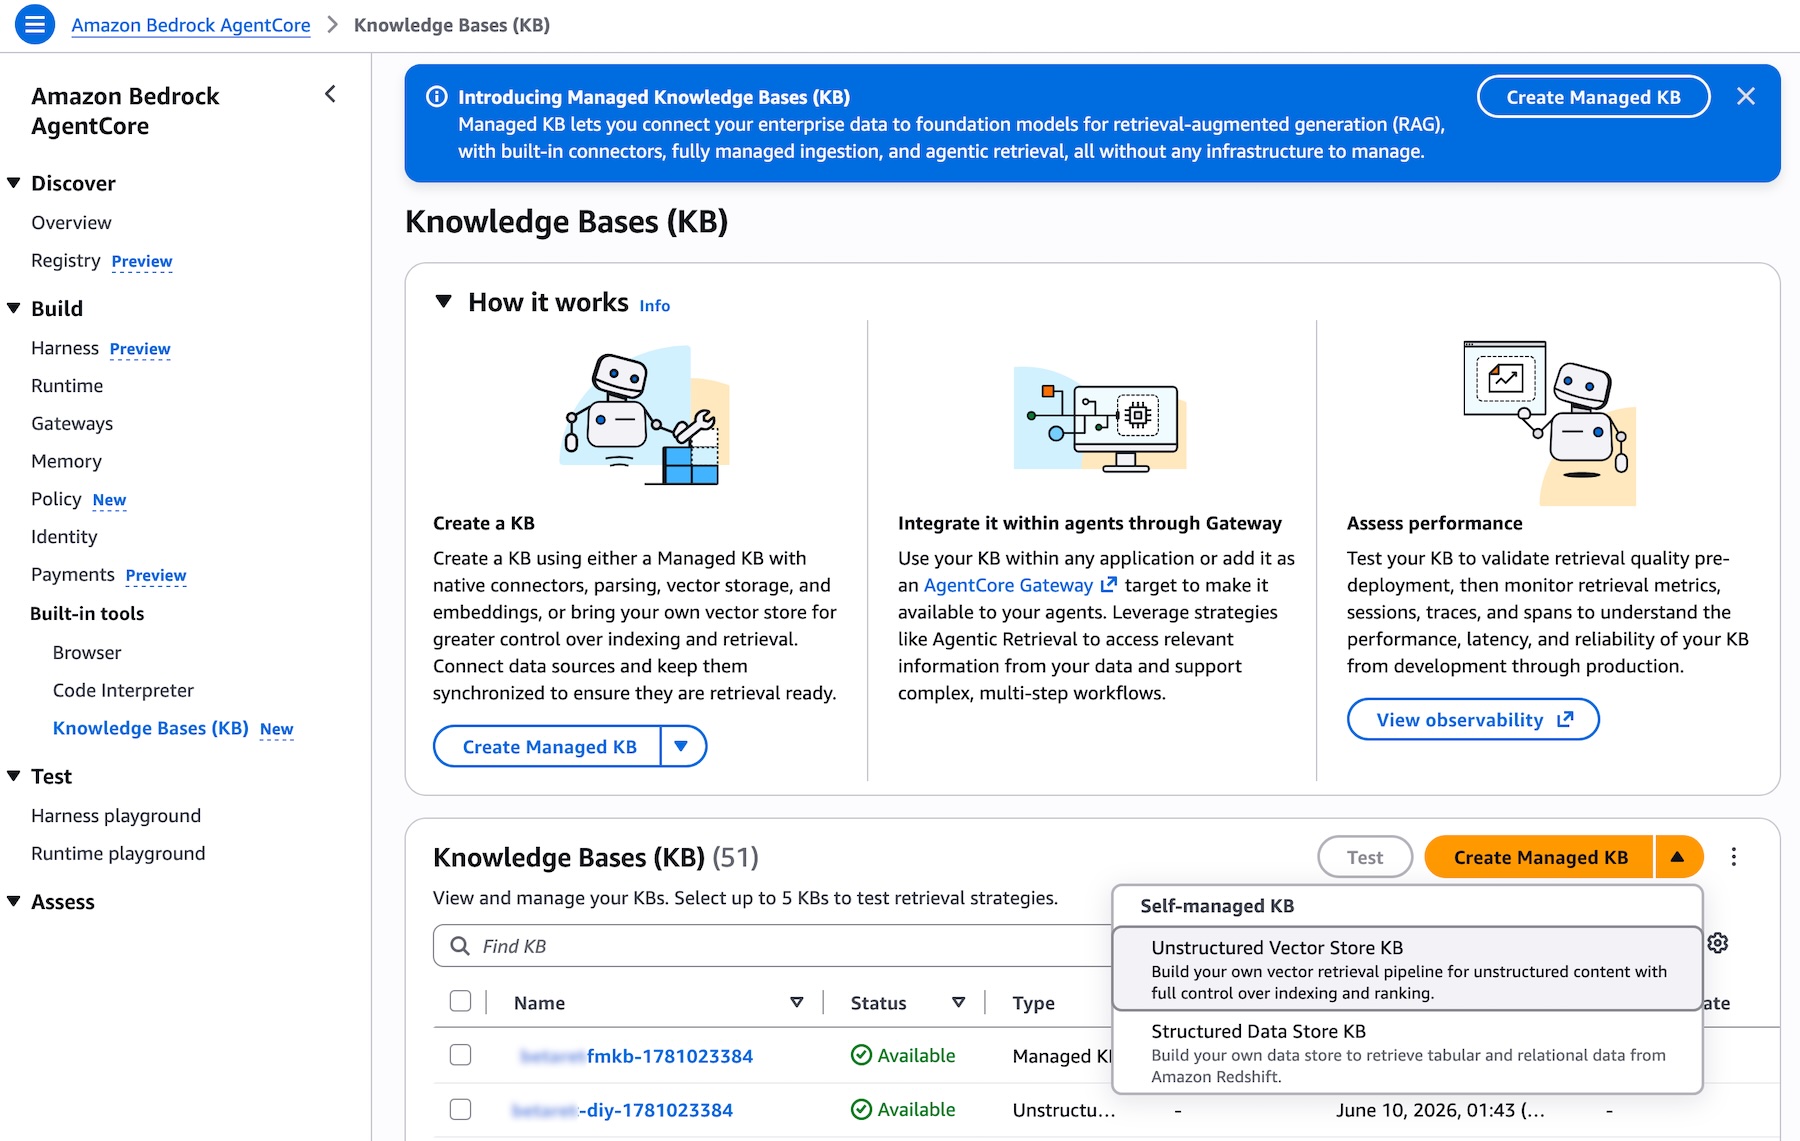
Creating a Managed Knowledge Base is straightforward. Navigate to the Amazon Bedrock AgentCore console or the Amazon Bedrock console, open the Knowledge Bases page, and choose Create Managed KB. The experience is the same in both consoles. You will see that Unstructured Vector Store KB is now available as the recommended option, alongside the other knowledge base types you may already be familiar with:

Picture 1 – Knowledge Bases list page in the Amazon Bedrock AgentCore console showing the Type column with different KB types and the Create Managed KB button

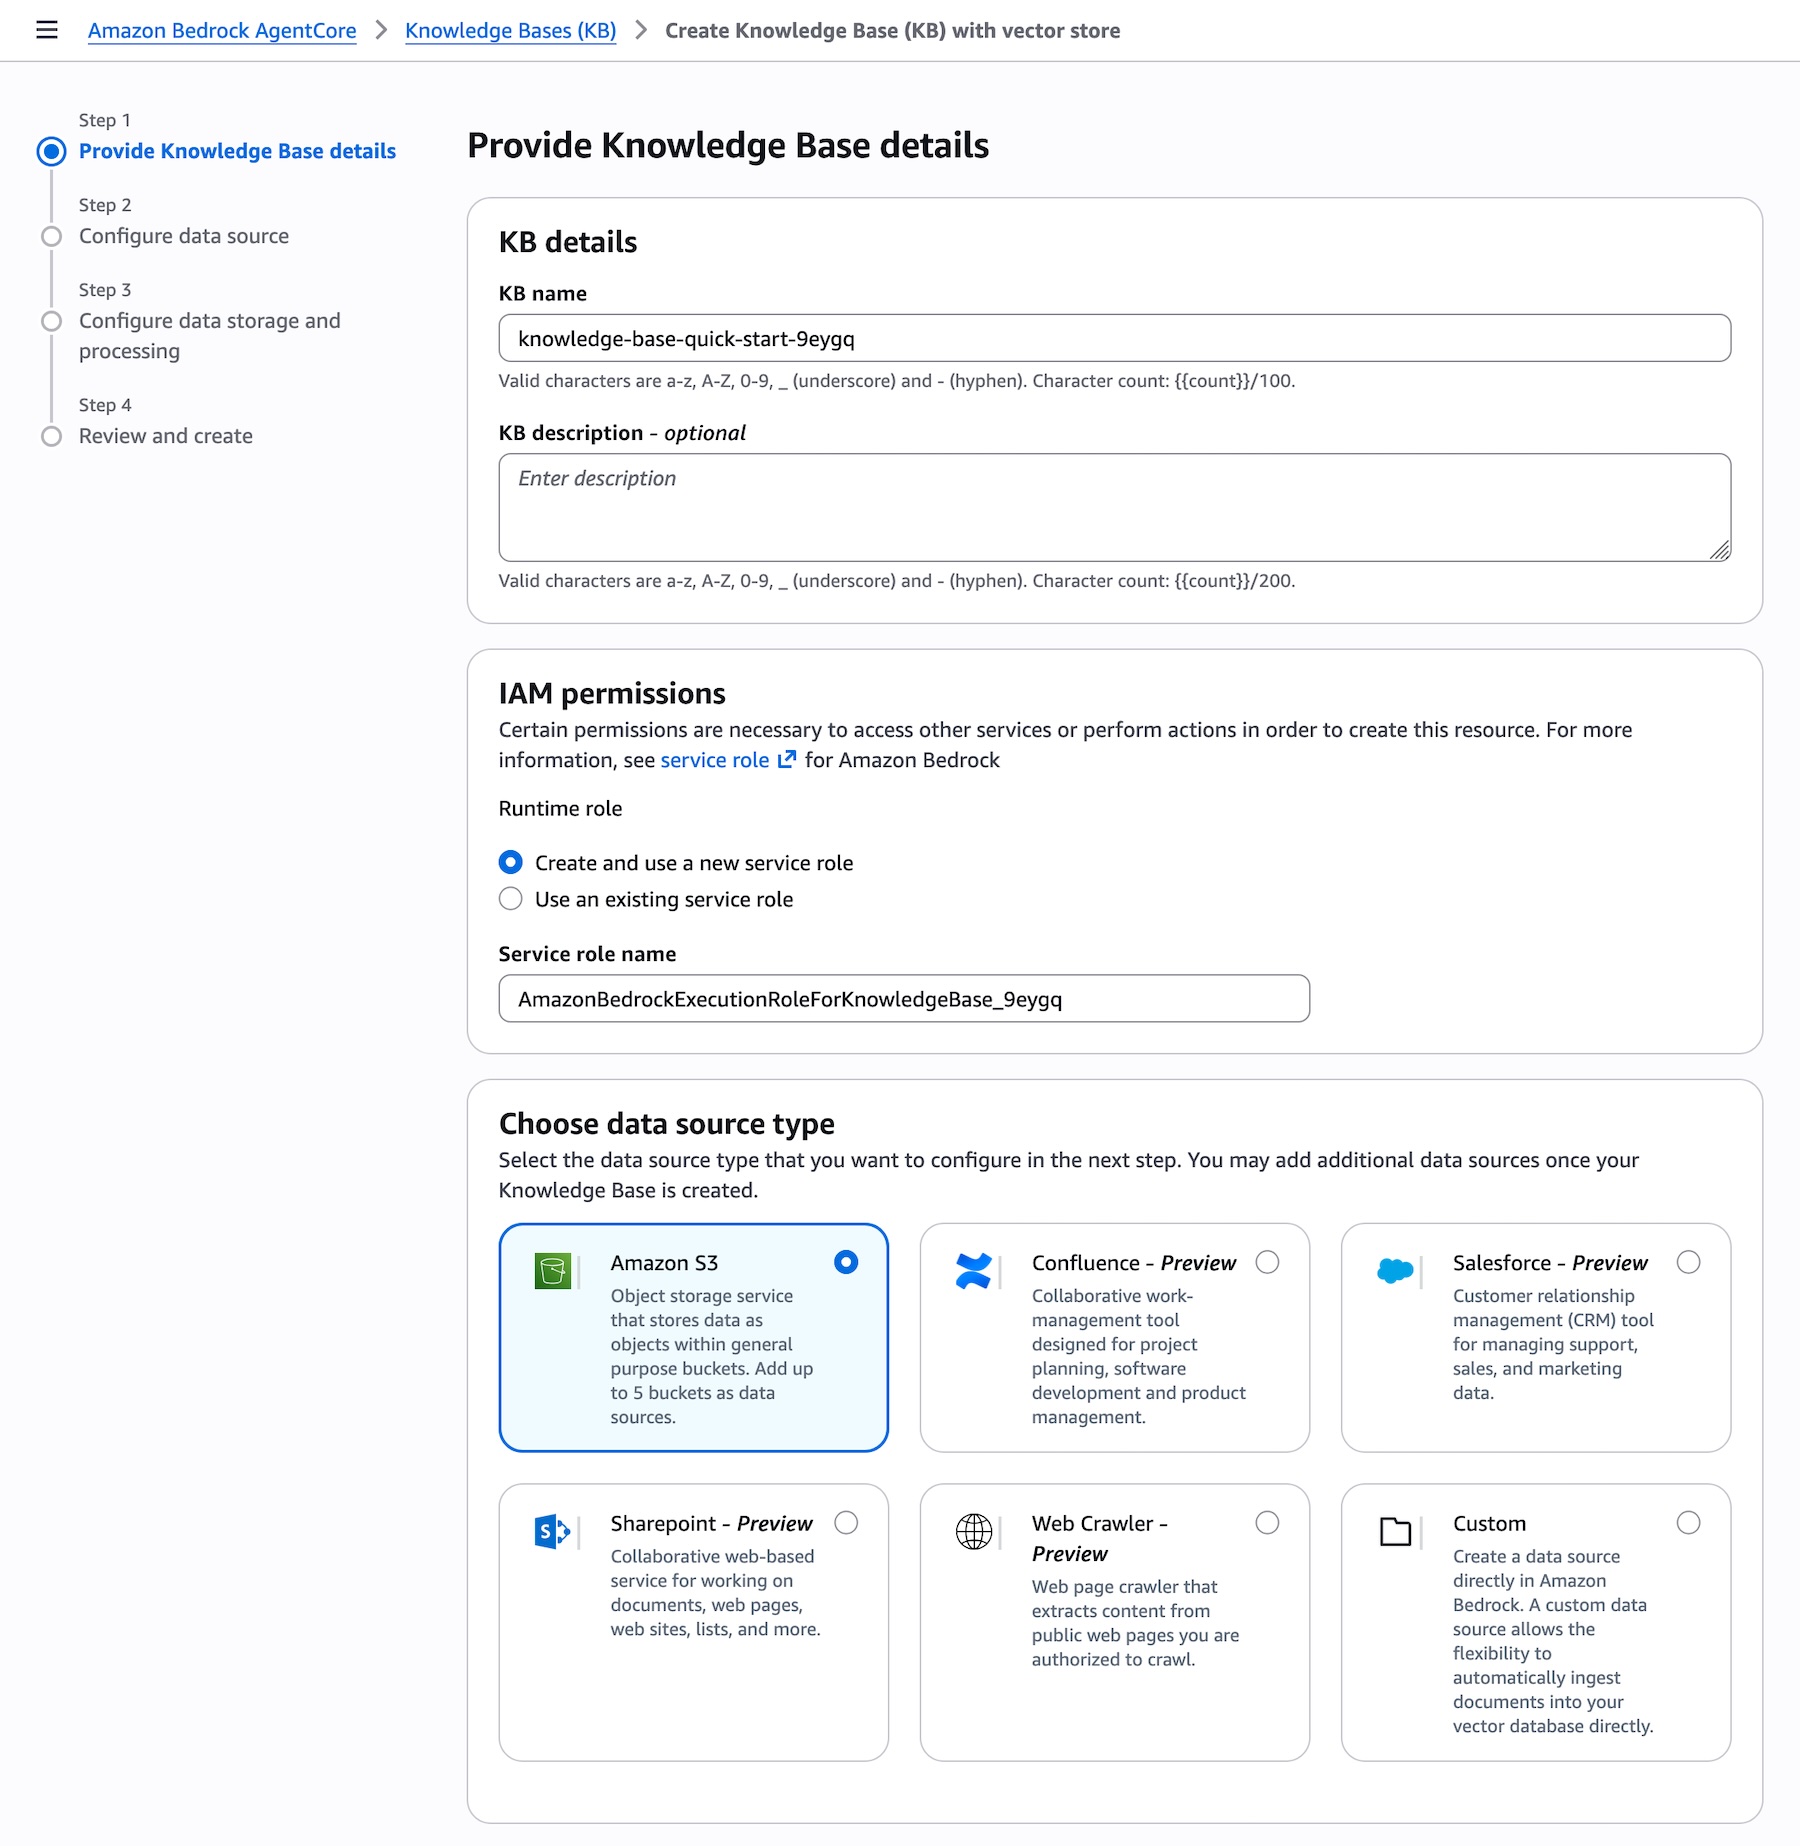
When creating a new Knowledge Bases, you can connect to your enterprise data sources by choosing from the list of supported connectors directly from a dropdown. AWS Identity and Access Management (IAM) roles are automatically created, and you can choose to edit these permissions if needed:

Picture 2 – Create Knowledge Base page showing the Data source dropdown expanded with all supported connectors: Amazon S3, Confluence, Custom, Google Drive, One Drive, SharePoint, and Web Crawler

An optimized set of defaults will be presented, allowing you to create your knowledge base in just a few clicks. Once the data is synced, you can integrate the knowledge base with your agent or provide it as a tool for your foundation model and start querying.

Smart Parsing for accurate data ingestion
One of the key challenges in building knowledge bases is preparing diverse data types for accurate retrieval. Once you point Managed Knowledge Base at your data sources, Smart Parsing automatically determines the optimal parsing strategy for each data type and connector, no extra configuration is required.

Smart Parsing combines multiple techniques:

  • Connector-specific data models – Optimized handling for each data source. For example, the Web Crawler connector preserves HTML structure including embedded images and tables, ensuring rich content is not dropped during ingestion. SharePoint connectors maintain document hierarchy and relationships between files.
  • Multimodal processing – Automatic detection and processing of different content types within documents. The system identifies bounding boxes in documents, then sends them to foundation models for data extraction, captioning, and scene description in video files.
  • Optimized chunking – Smart Parsing leverages foundation models to understand document structure and extract meaningful content, ensuring that complex documents with mixed formats are properly indexed. Intelligent defaults balance retrieval accuracy with performance based on document type and content structure, while advanced users can customize chunking strategies when needed.

This automated approach eliminates weeks of experimentation typically required to achieve production-quality retrieval accuracy, while still preserving the flexibility to customize when needed.

Using Agentic Retriever for complex queries
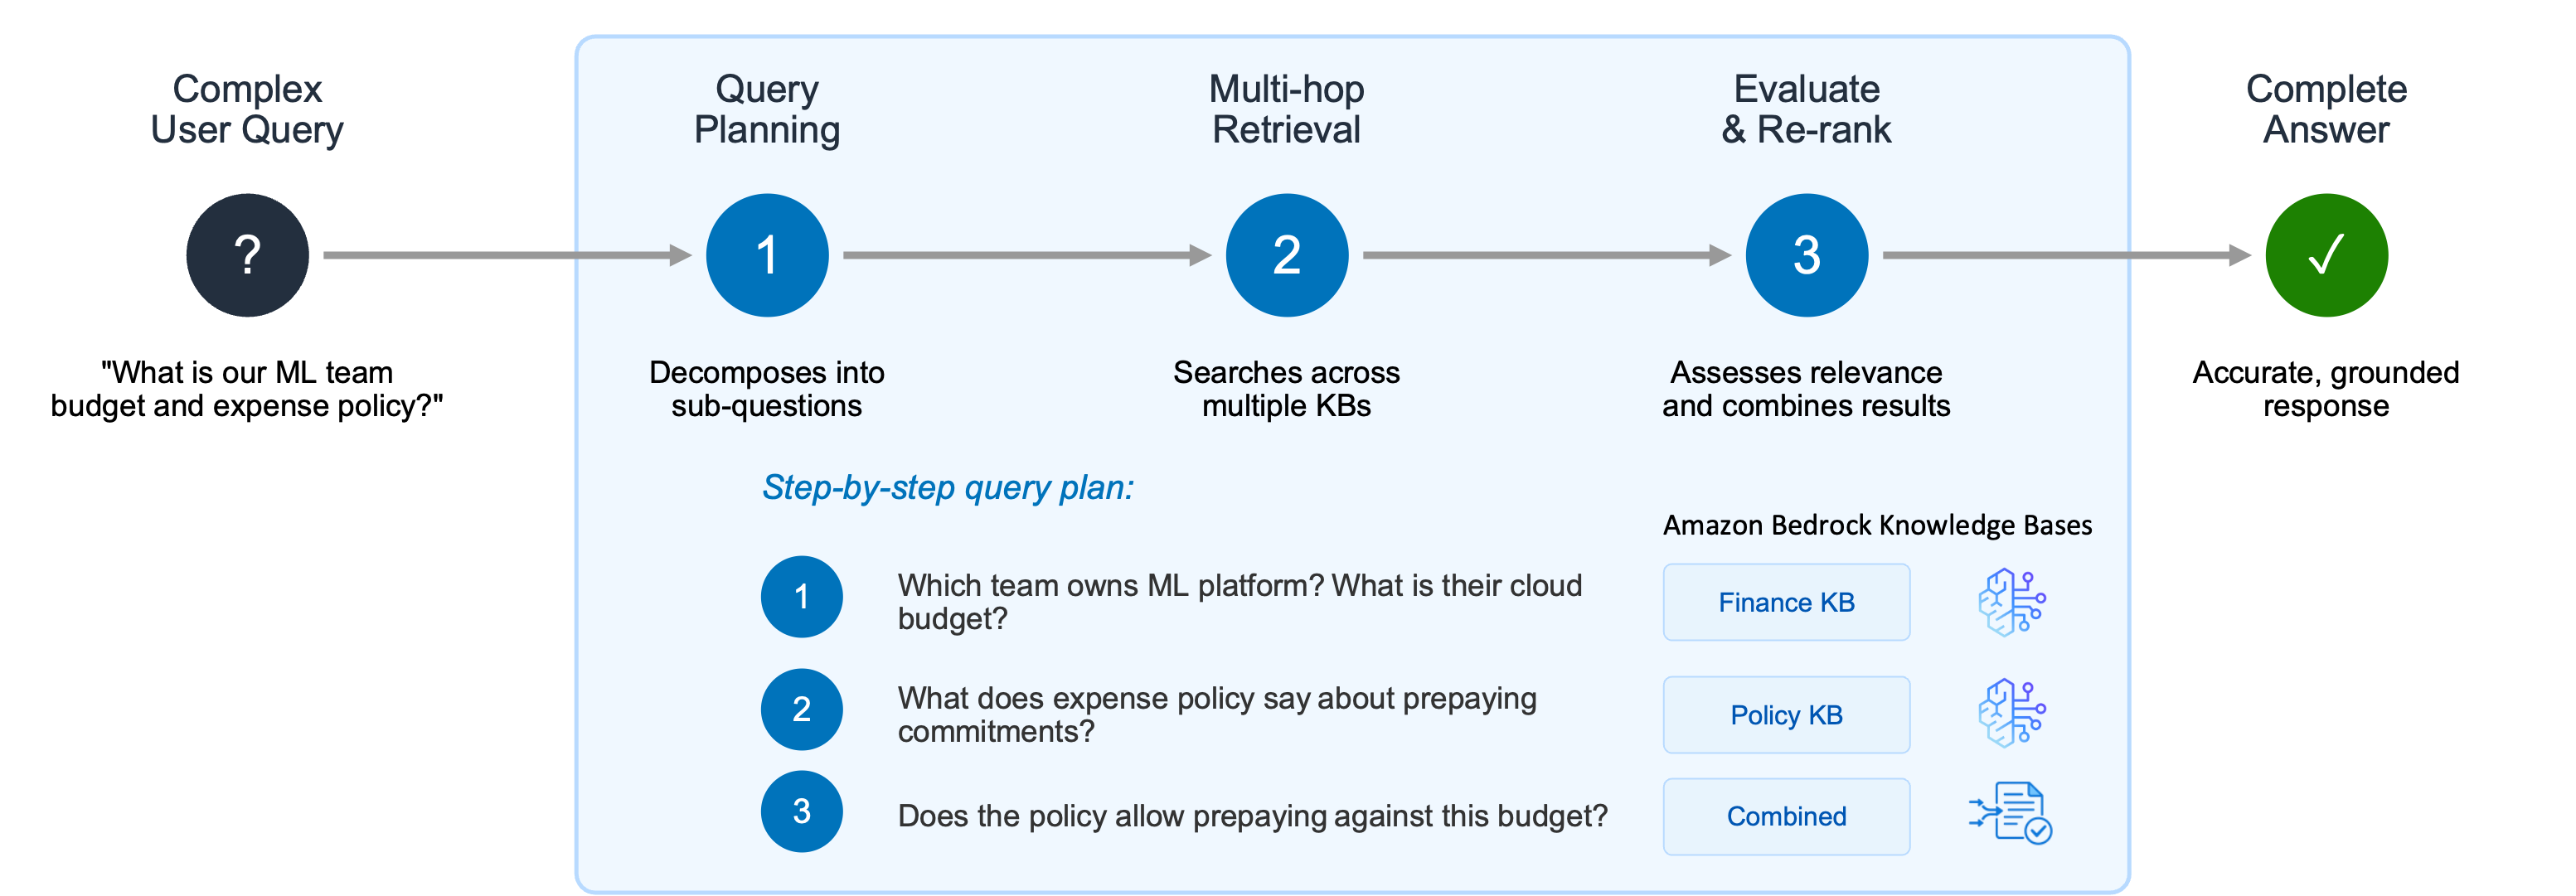
After your data is ingested, you can start querying your knowledge base. Generative AI applications often struggle with complex user queries that require reasoning, recursive multi-step retrieval, and intermediate evaluations of results. Consider a user asking two related questions: “What is the cloud infrastructure budget for the ML platform team?” and “Does our expense policy allow prepaying annual commitments?” A single retrieval step might surface documents about the ML platform team but fail to connect the budget information with the expense policy needed to fully answer the question.

Picture 3 – Agentic Retriever decomposes complex user queries into a step-by-step plan, performing multi-hop retrieval across multiple knowledge bases and combining results to deliver accurate, grounded responses

Agentic Retriever solves this by creating a step-by-step query plan: 1. Which team owns the ML platform, and what is their cloud infrastructure budget? 2. What does the expense policy say about prepaying annual commitments? 3. Does the policy allow the ML platform team to prepay against this budget?

The system performs multi-hop retrieval and reasoning at each step, and once it has gathered sufficient relevant passages, it stops the search process and returns the top results. By abstracting away the complexity of building a separate multi-hop reasoning pipeline, this approach dramatically improves accuracy for complex queries while letting developers focus on their agentic search applications instead of orchestration logic.

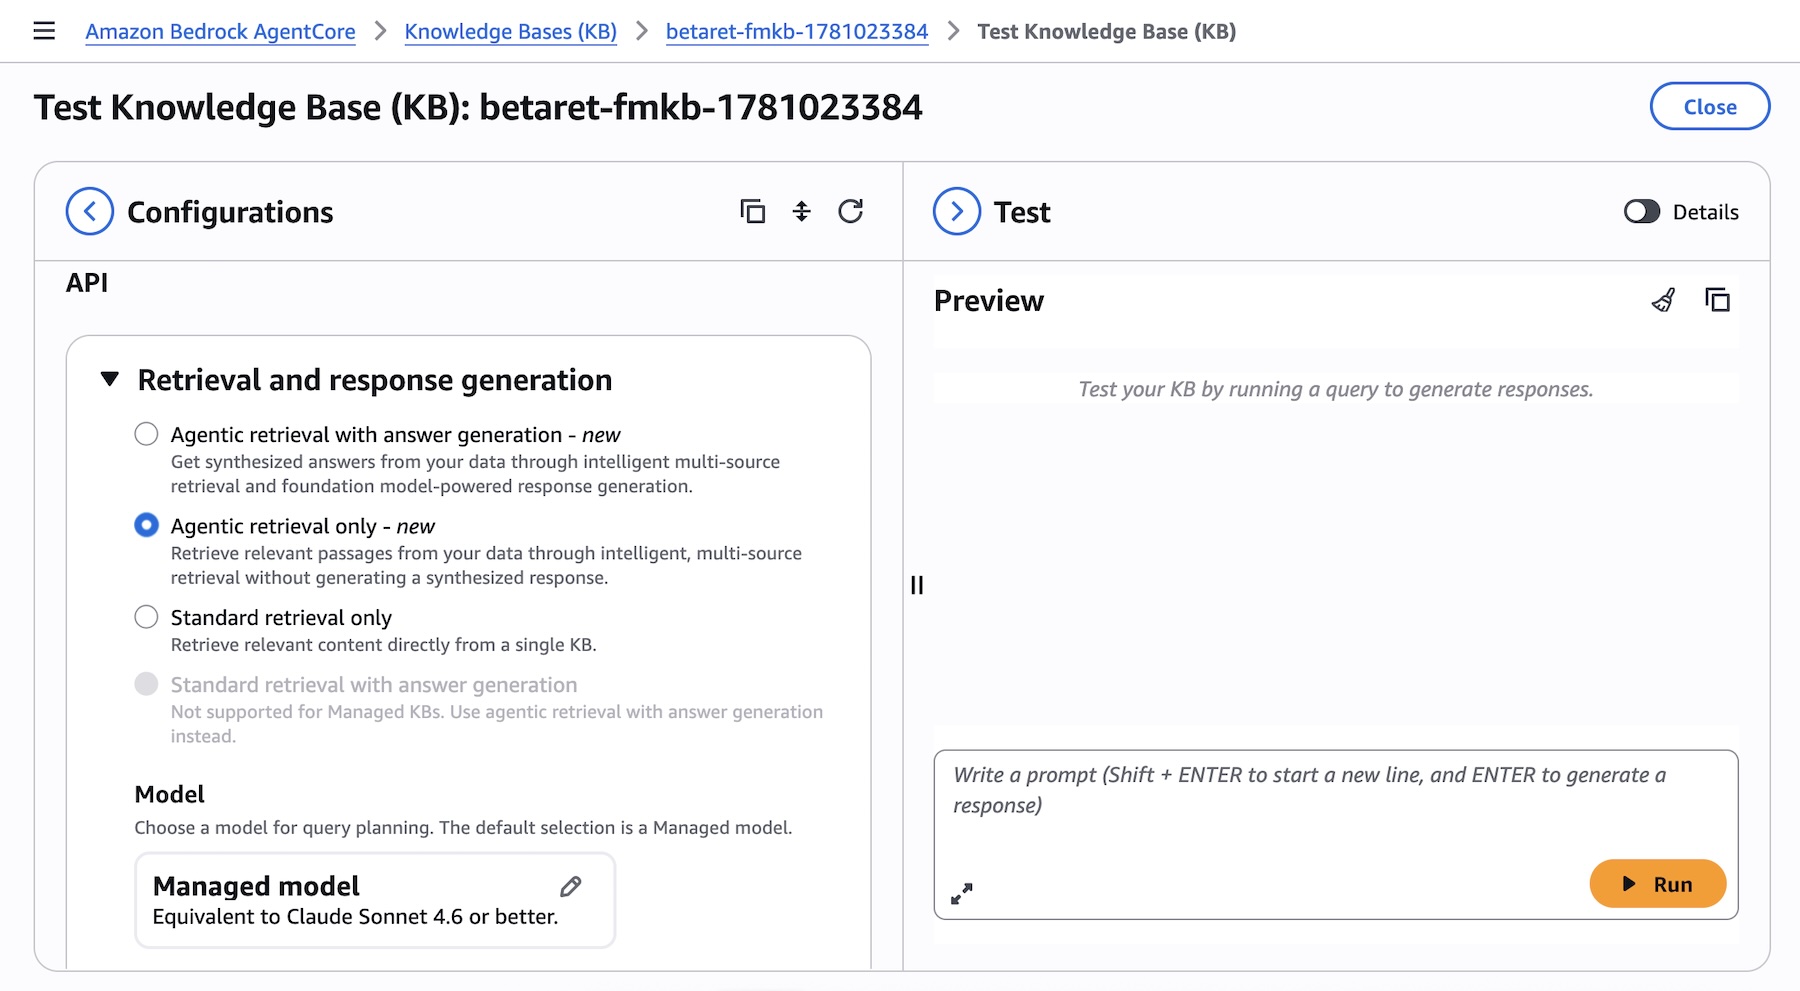
You can try Agentic Retriever directly from the test panel of your knowledge base in the Amazon Bedrock AgentCore console. Select Agentic retrieval only as the retrieval type to let the system automatically plan and execute multi-step queries across your knowledge bases:

Picture 4 – Test Knowledge Base panel showing Agentic retrieval with answer generation selected as the retrieval type, with model selection and maximum agentic iterations options

Enabling MCP with Bedrock AgentCore
Amazon Bedrock Managed Knowledge Base seamlessly integrates with AgentCore Gateway as a native target type. This integration eliminates the need for manual integration and provides built-in observability, policy enforcement, and automatic permission management.

You can navigate to the Amazon Bedrock AgentCore console or SDK and create an AgentCore Gateway or select an existing one. When adding targets to your gateway, you will find Knowledge Base as a new pre-built target type alongside other options such as MCP server, Lambda ARN, REST API, and other integrations. Simply select your knowledge base ID to expose it through the gateway:

Picture 5 – Add targets page in AgentCore Gateway showing Knowledge Base as a new pre-built target type, with the knowledge base ID selector and runtime retrieval mode options

Add targets page in AgentCore Gateway showing Knowledge Base as a new pre-built target type, with the knowledge base ID selector and runtime retrieval mode options

Gateway exposes the standard Model Context Protocol (MCP), so the knowledge base tools are automatically discovered by clients from any MCP-compatible framework, including Strands Agents, LangChain, CrewAI, LlamaIndex, and LangGraph. No custom integration code is required.

Model choice and flexibility
Amazon Bedrock Managed Knowledge Base preserves the flexibility developers expect from Amazon Bedrock. Every foundation model available on Bedrock can power the generation step, and developers can select from different embedding and re-ranking models to optimize retrieval for their specific use case, enabling teams to fine-tune accuracy and cost-performance without changing infrastructure.

Unlike managed solutions that lock you into specific model providers, Amazon Bedrock Managed Knowledge Base separates the infrastructure management (connectors, parsing, storage, retrieval orchestration) from model selection. This means you can:

  • Take advantage of the latest models – Adopt the latest embedding, re-ranking, and foundation models as they become available to improve accuracy, latency, and cost for your application without rebuilding your RAG pipeline.
  • Optimize for price-performance – Choose smaller, faster models for simple queries and more capable models for complex reasoning tasks, all using the same knowledge base infrastructure.
  • Use Bedrock embedding models – While Smart Parsing provides optimized defaults, you can configure Bedrock embedding models when your domain requires specialized semantic understanding.
  • Maintain consistency with existing applications – If you’re already using Bedrock Knowledge Bases APIs (Retrieve, StartIngest, StopIngest, IngestKnowledgeBaseDocuments), Managed Knowledge Base uses the same APIs, so migration requires no code changes, just point to the new knowledge base ID.

This approach ensures you can spend time on your generative AI application without losing the ability to change models based on evolving requirements or new model capabilities.

Get started today
Amazon Bedrock Managed Knowledge Base is available today in the US East (N. Virginia), US West (Oregon), Asia Pacific (Sydney, Tokyo), Europe (Dublin, Frankfurt, London), and AWS GovCloud (US-West) Regions. For Regional availability and future roadmap, visit AWS Capabilities by Region.

With Bedrock Managed Knowledge Base, you pay for what you use with no upfront commitments. Pricing is based on two dimensions: the size of indexed data stored and the number of retrievals performed (on-demand). For detailed pricing information, visit the Amazon Bedrock pricing page. Bedrock is also a part of the AWS Free Tier that new AWS customers can use to get started at no cost and explore key AWS services.

These capabilities work with any open source framework such as CrewAI, LangGraph, LlamaIndex, and Strands Agents, and with any foundation model. Bedrock services can be used together or independently, and you can get started using your favorite AI-assisted development environment with the AgentCore open source MCP server.

To learn more and get started quickly, visit the Bedrock Knowledge Bases Developer Guide.

Daniel Abib

Announcing Web Search on Amazon Bedrock AgentCore: Ground your AI agents in current, accurate web knowledge

Post Syndicated from Channy Yun (윤석찬) original https://aws.amazon.com/blogs/aws/announcing-web-search-on-amazon-bedrock-agentcore-ground-your-ai-agents-in-current-accurate-web-knowledge/

Today, we’re announcing the general availability of Web Search on Amazon Bedrock AgentCore, a fully managed tool that enables agents to ground responses in current, cited web knowledge with zero data egress from customer’s secured AWS environment.

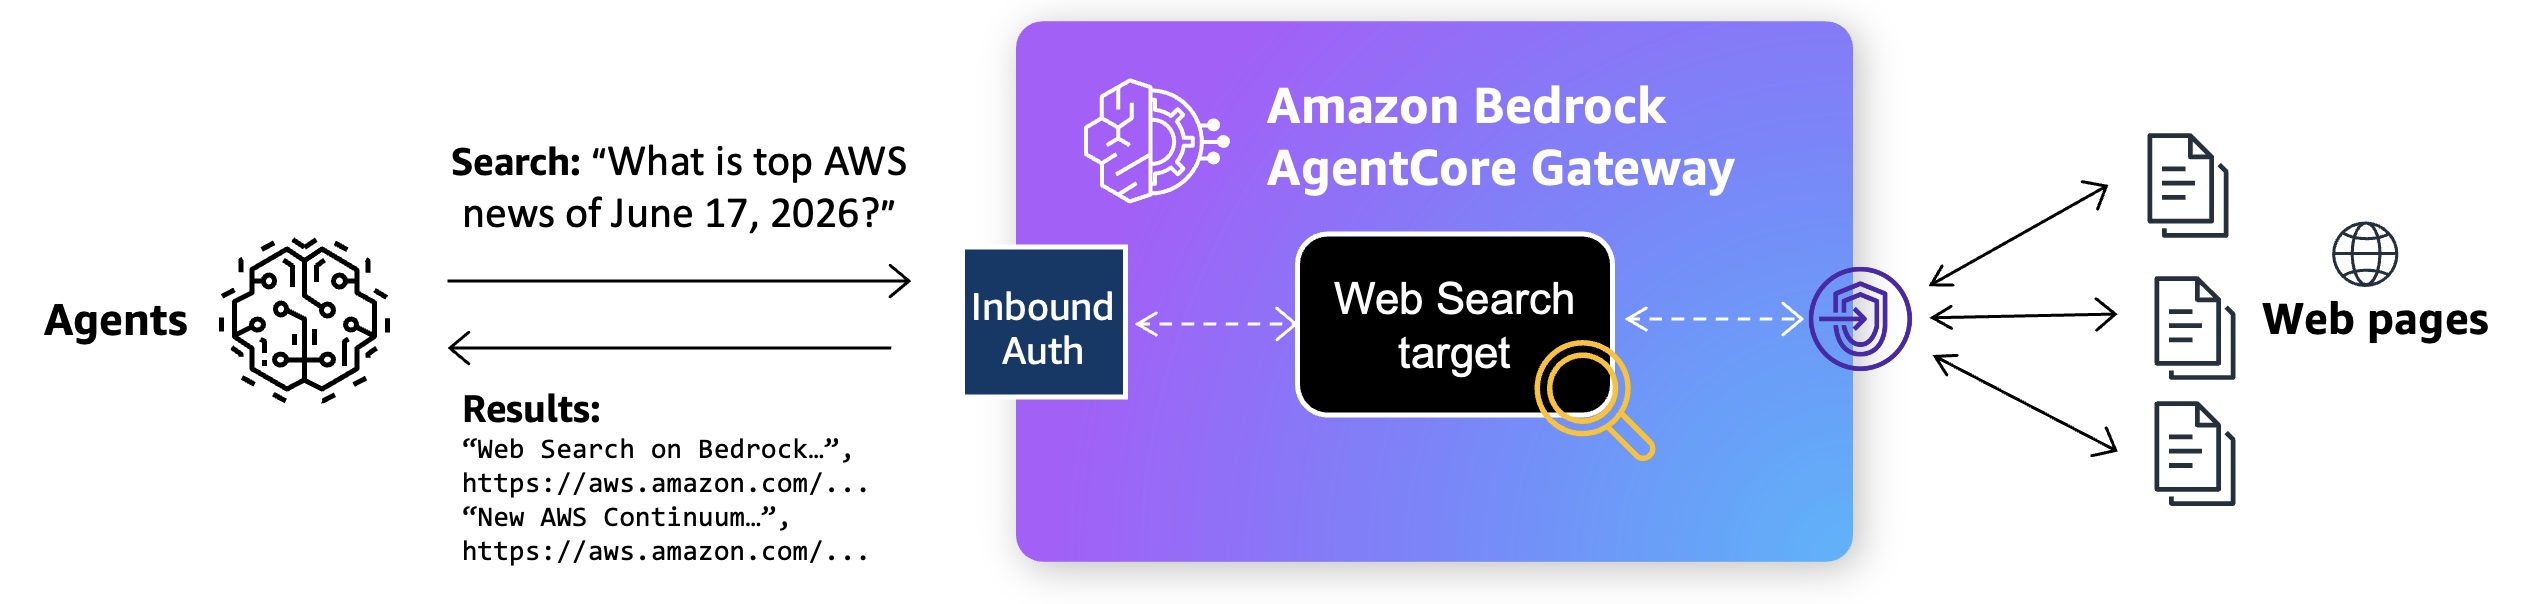
Web Search uses a built-in connector target on Bedrock AgentCore Gateway using the Model Context Protocol (MCP). Your agent sends a natural-language query, and Web Search returns most relevant snippets, source URLs, titles, and publication dates that the model can reason over to produce a grounded response.

It is built on Amazon’s search infrastructure, informed by years of experience powering agentic search experiences across Alexa+, Amazon Quick, and Kiro. It uses a multi-source grounding approach that combines Amazon’s web index with structured knowledge graph data. Beyond standard web results, this gives agents access to Amazon Knowledge Graph with verified facts, helping them retrieve more relevant and accurate responses than traditional web search alone.

With this launch, you can focus on building agents instead of manually adding web search to agents on Bedrock AgentCore and managing its infrastructure. Your AI agent looks at user question, retrieves the latest facts, and then takes any necessary action grounded in current developments beyond a model’s training data. You can also meet enterprise governance policies without sending user prompts and retrieval queries to external search API providers outside of AWS.

Web Search on Bedrock AgentCore in action
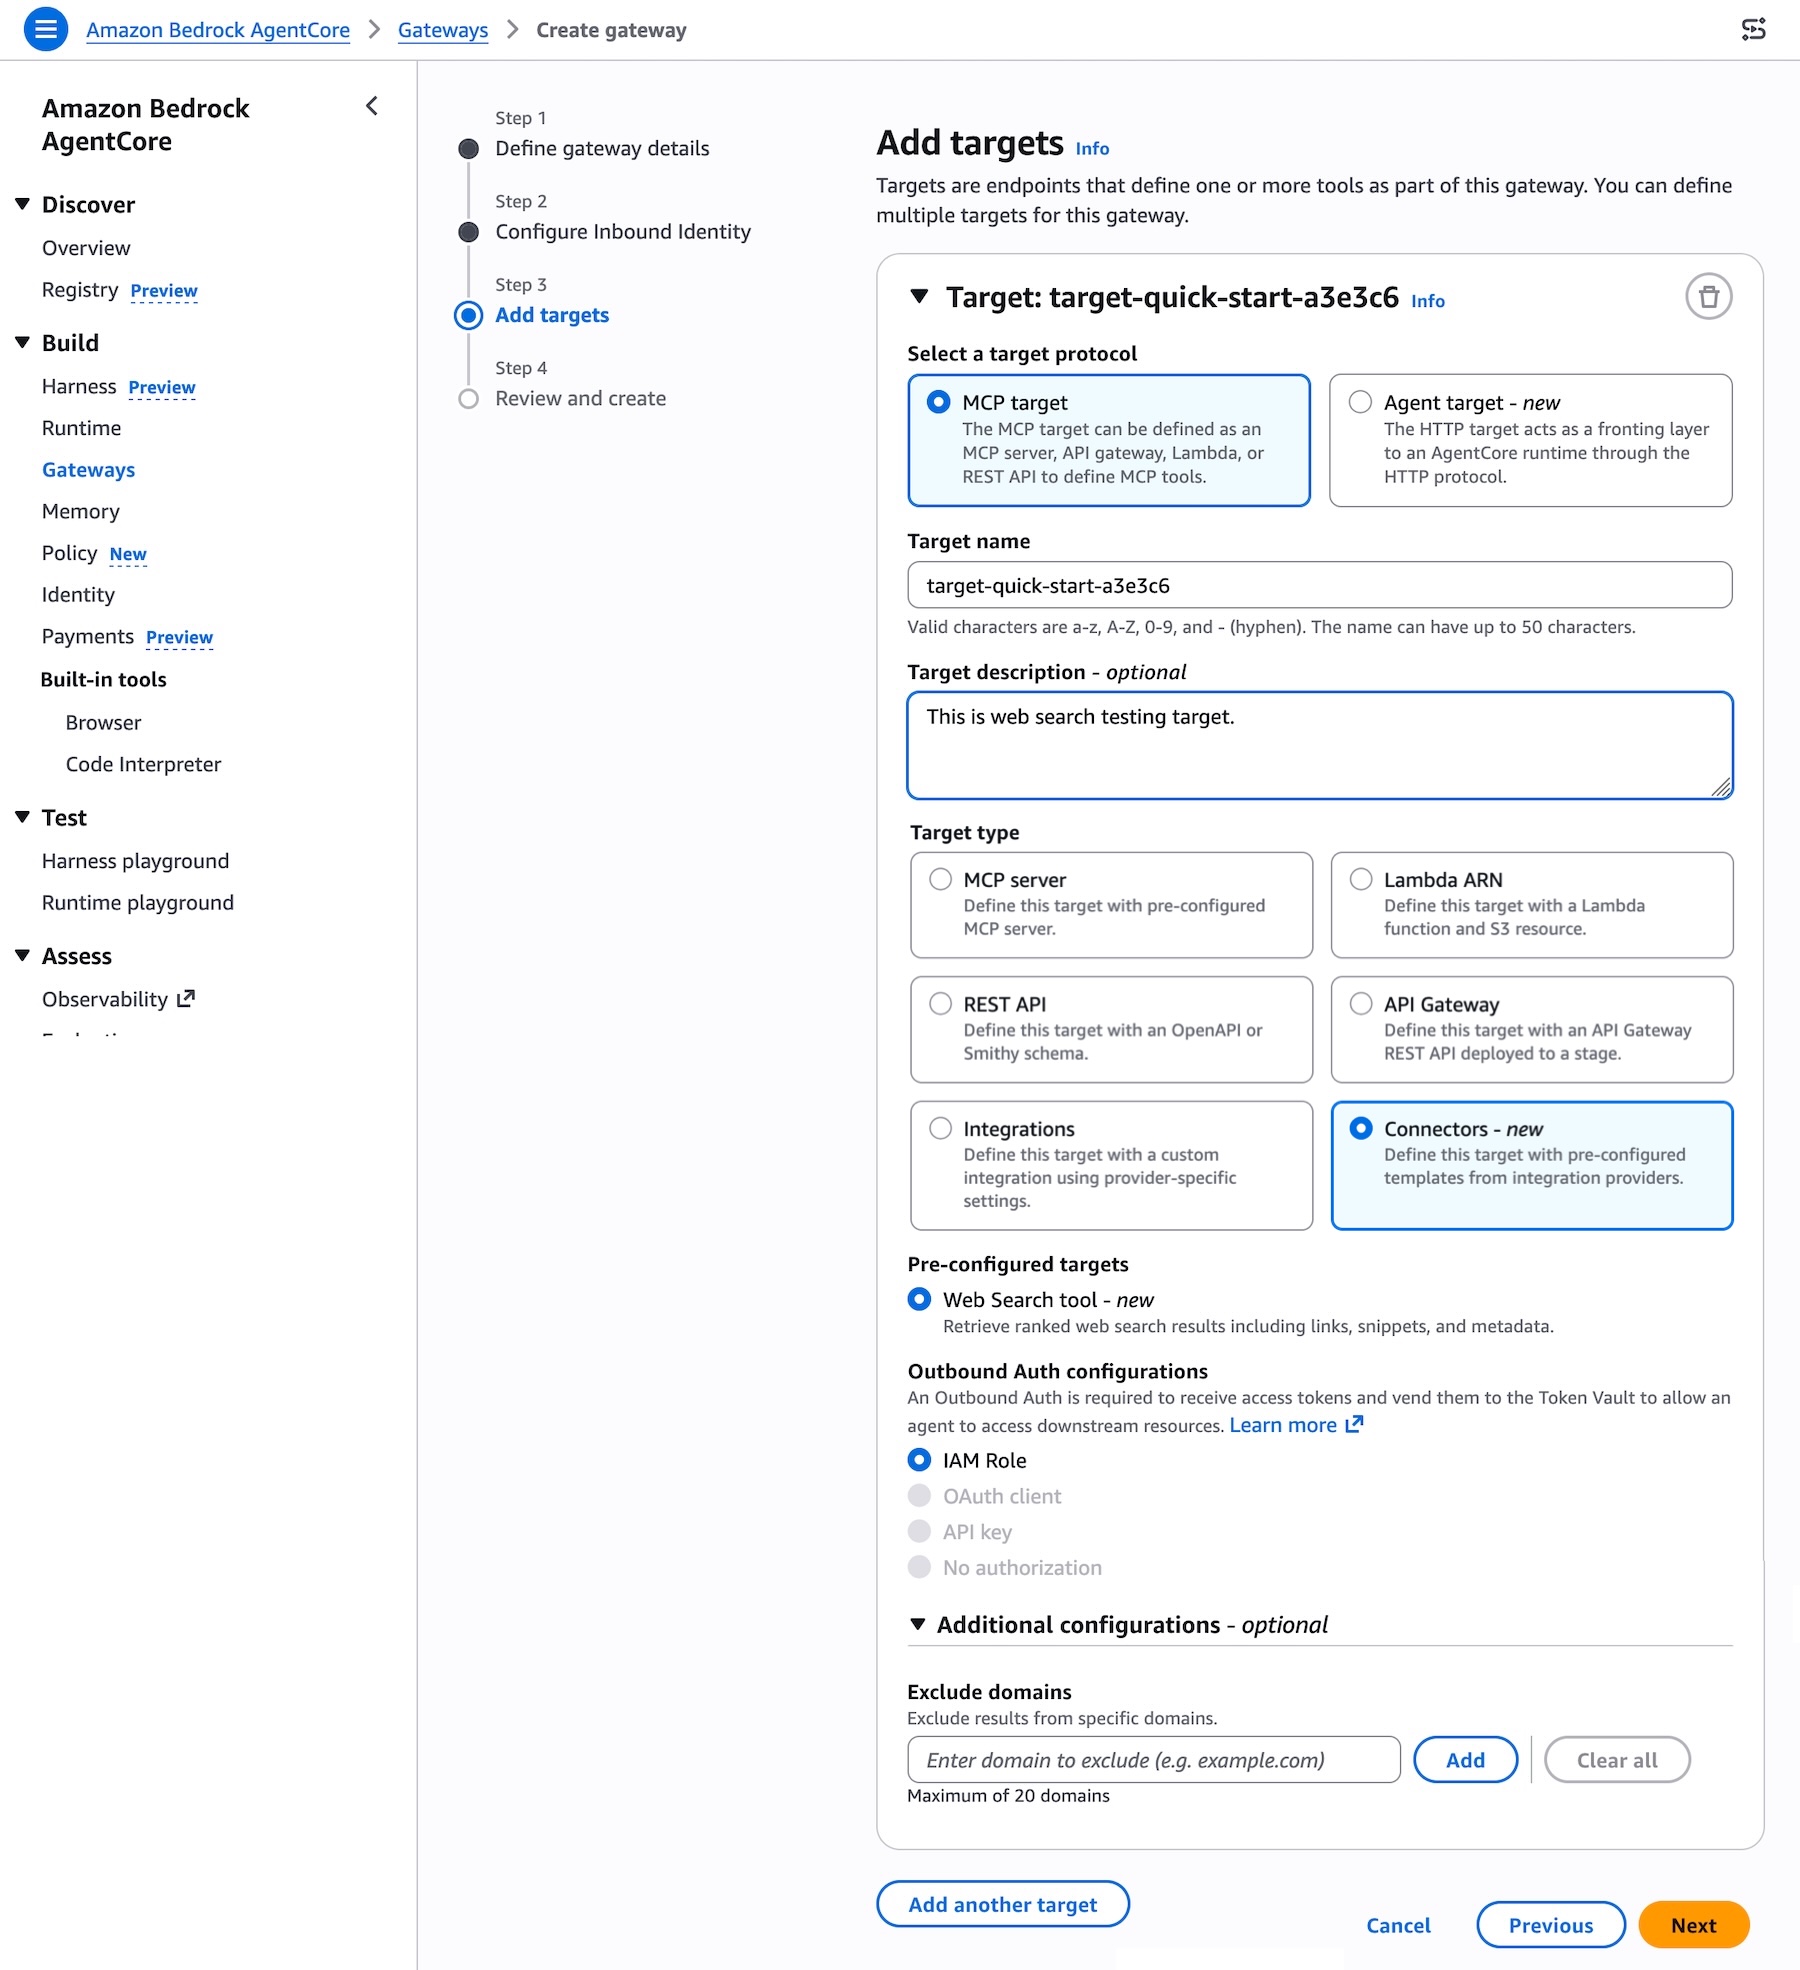
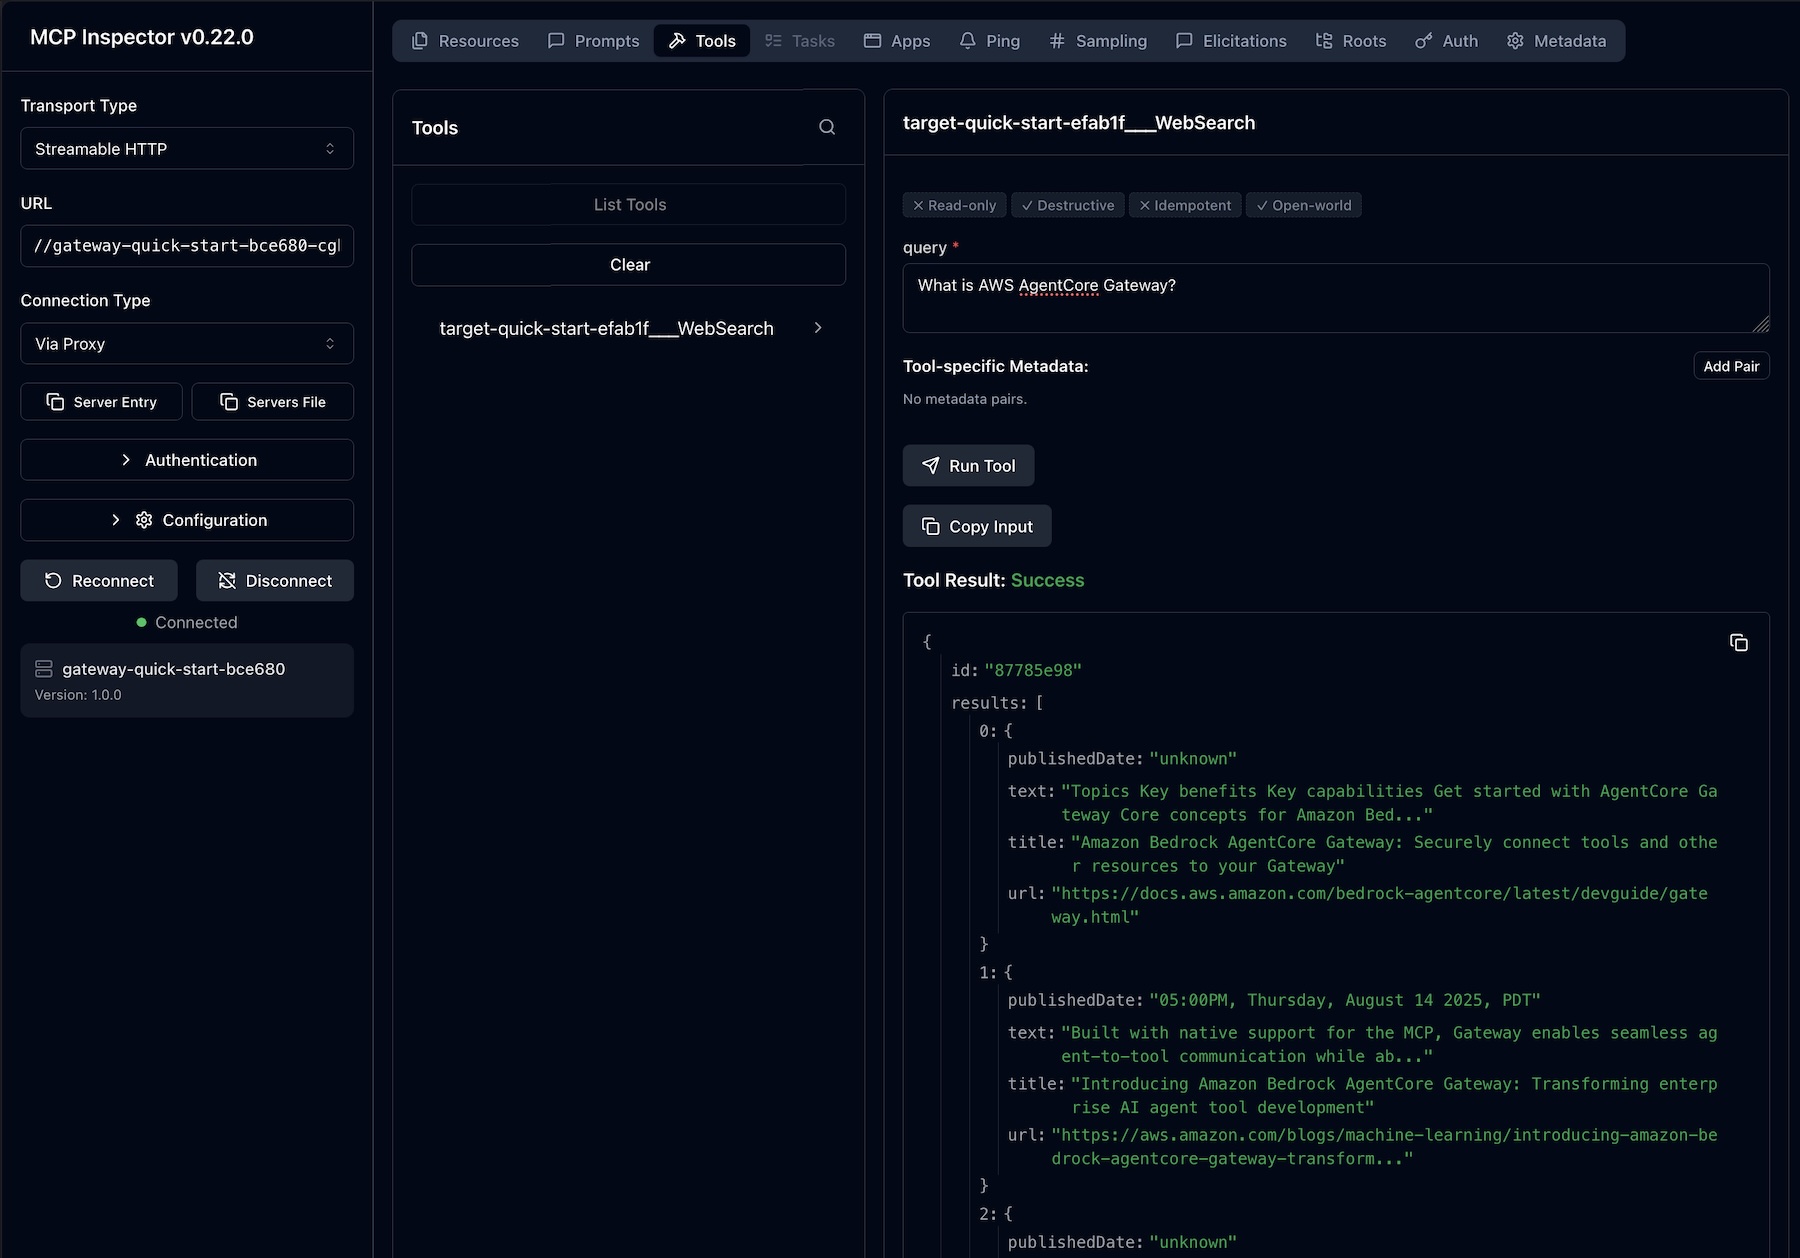
To get started, create the Bedrock AgentCore Gateway with Web Search tool target in the Bedrock AgentCore console. When the Gateway URL is created, you can interact with API call, Command Line Interface (CLI), or MCP Inspector.

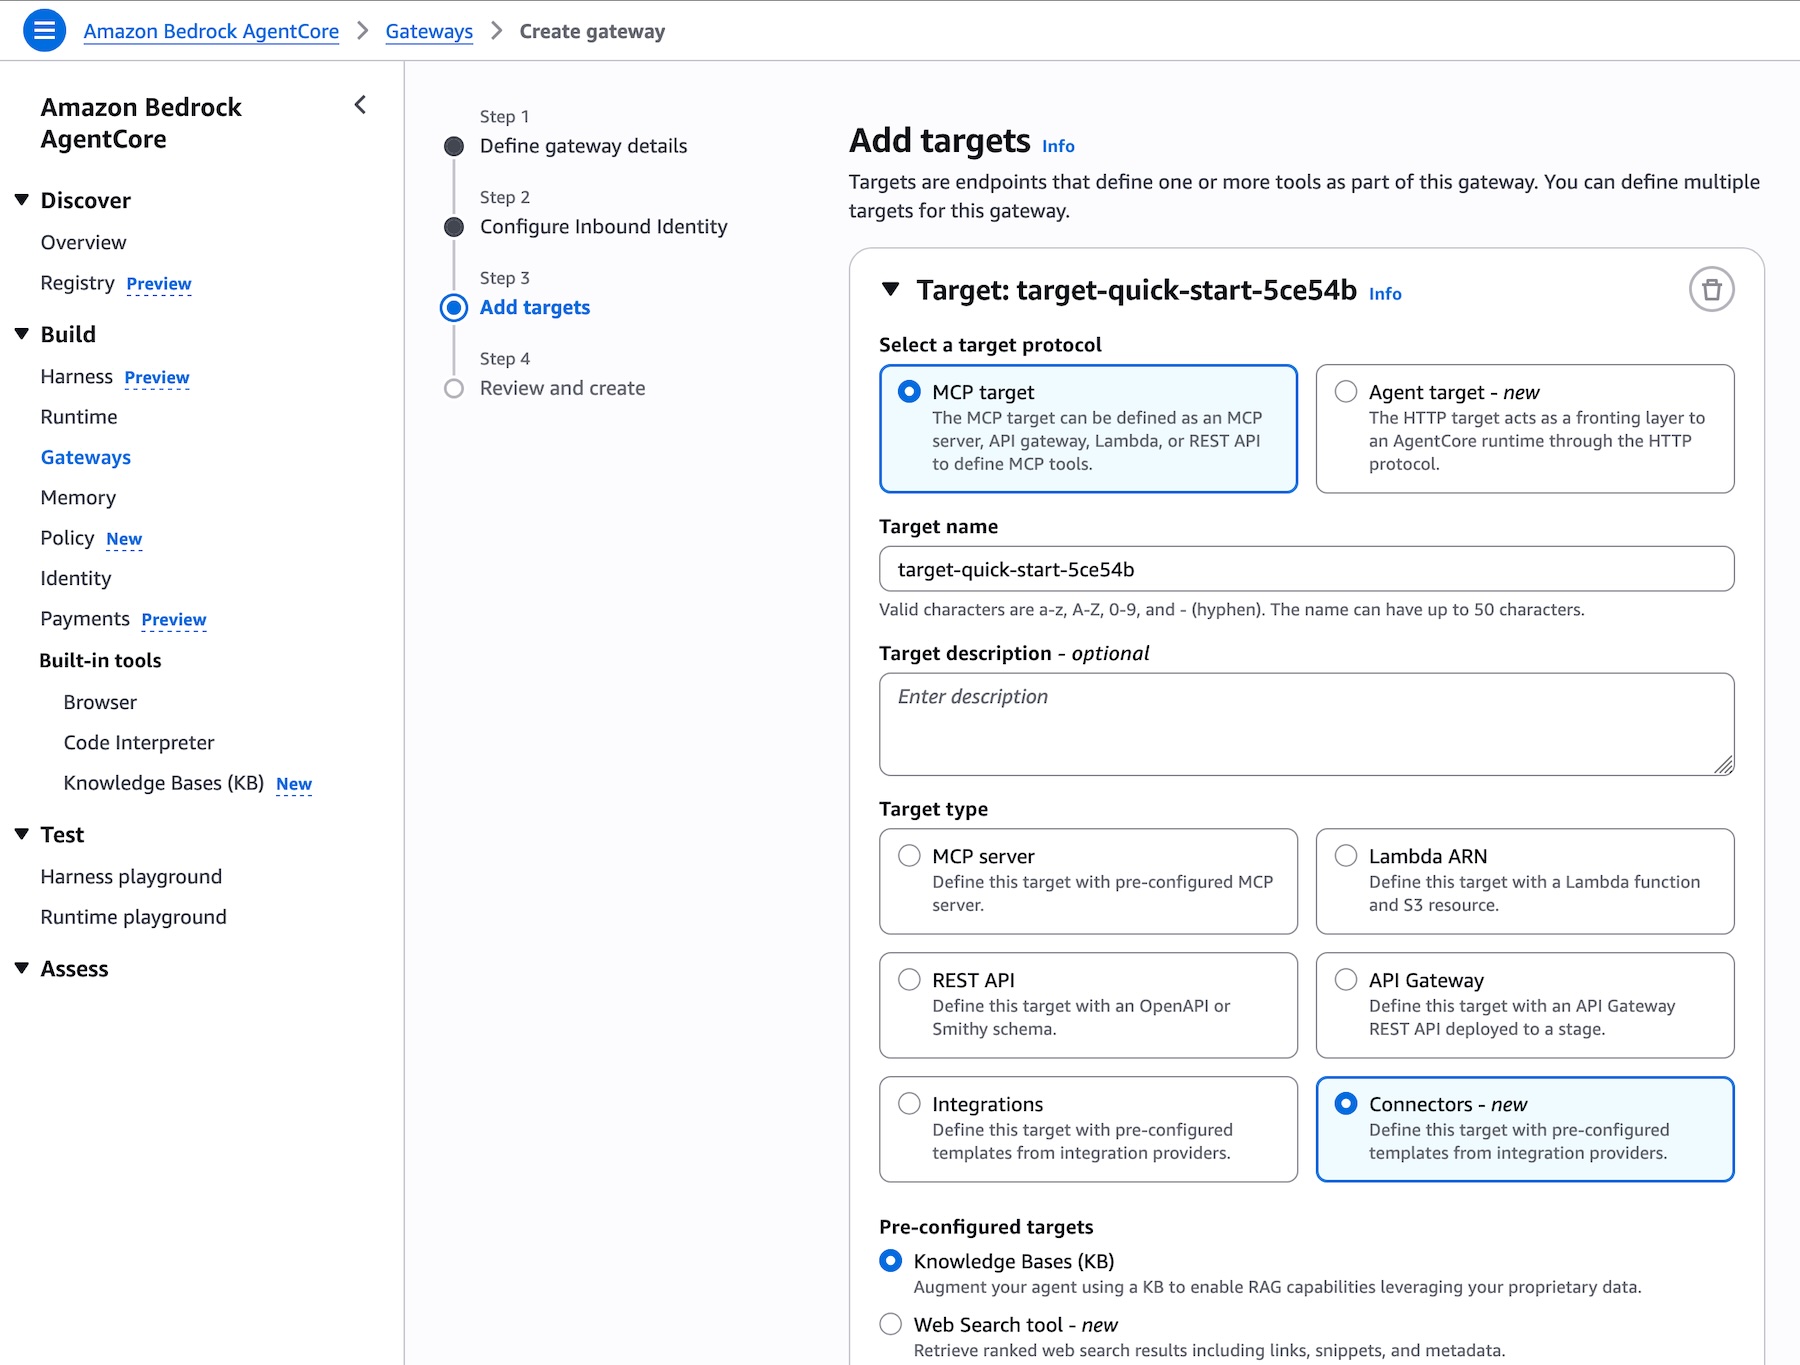
To add Web Search tool target when creating the Gateway, choose MCP target as a target protocol and Connectors as a target type. You can select the Web Search tool as a preconfigured target to retrieve most relevant web search results including links, snippets, and metadata.

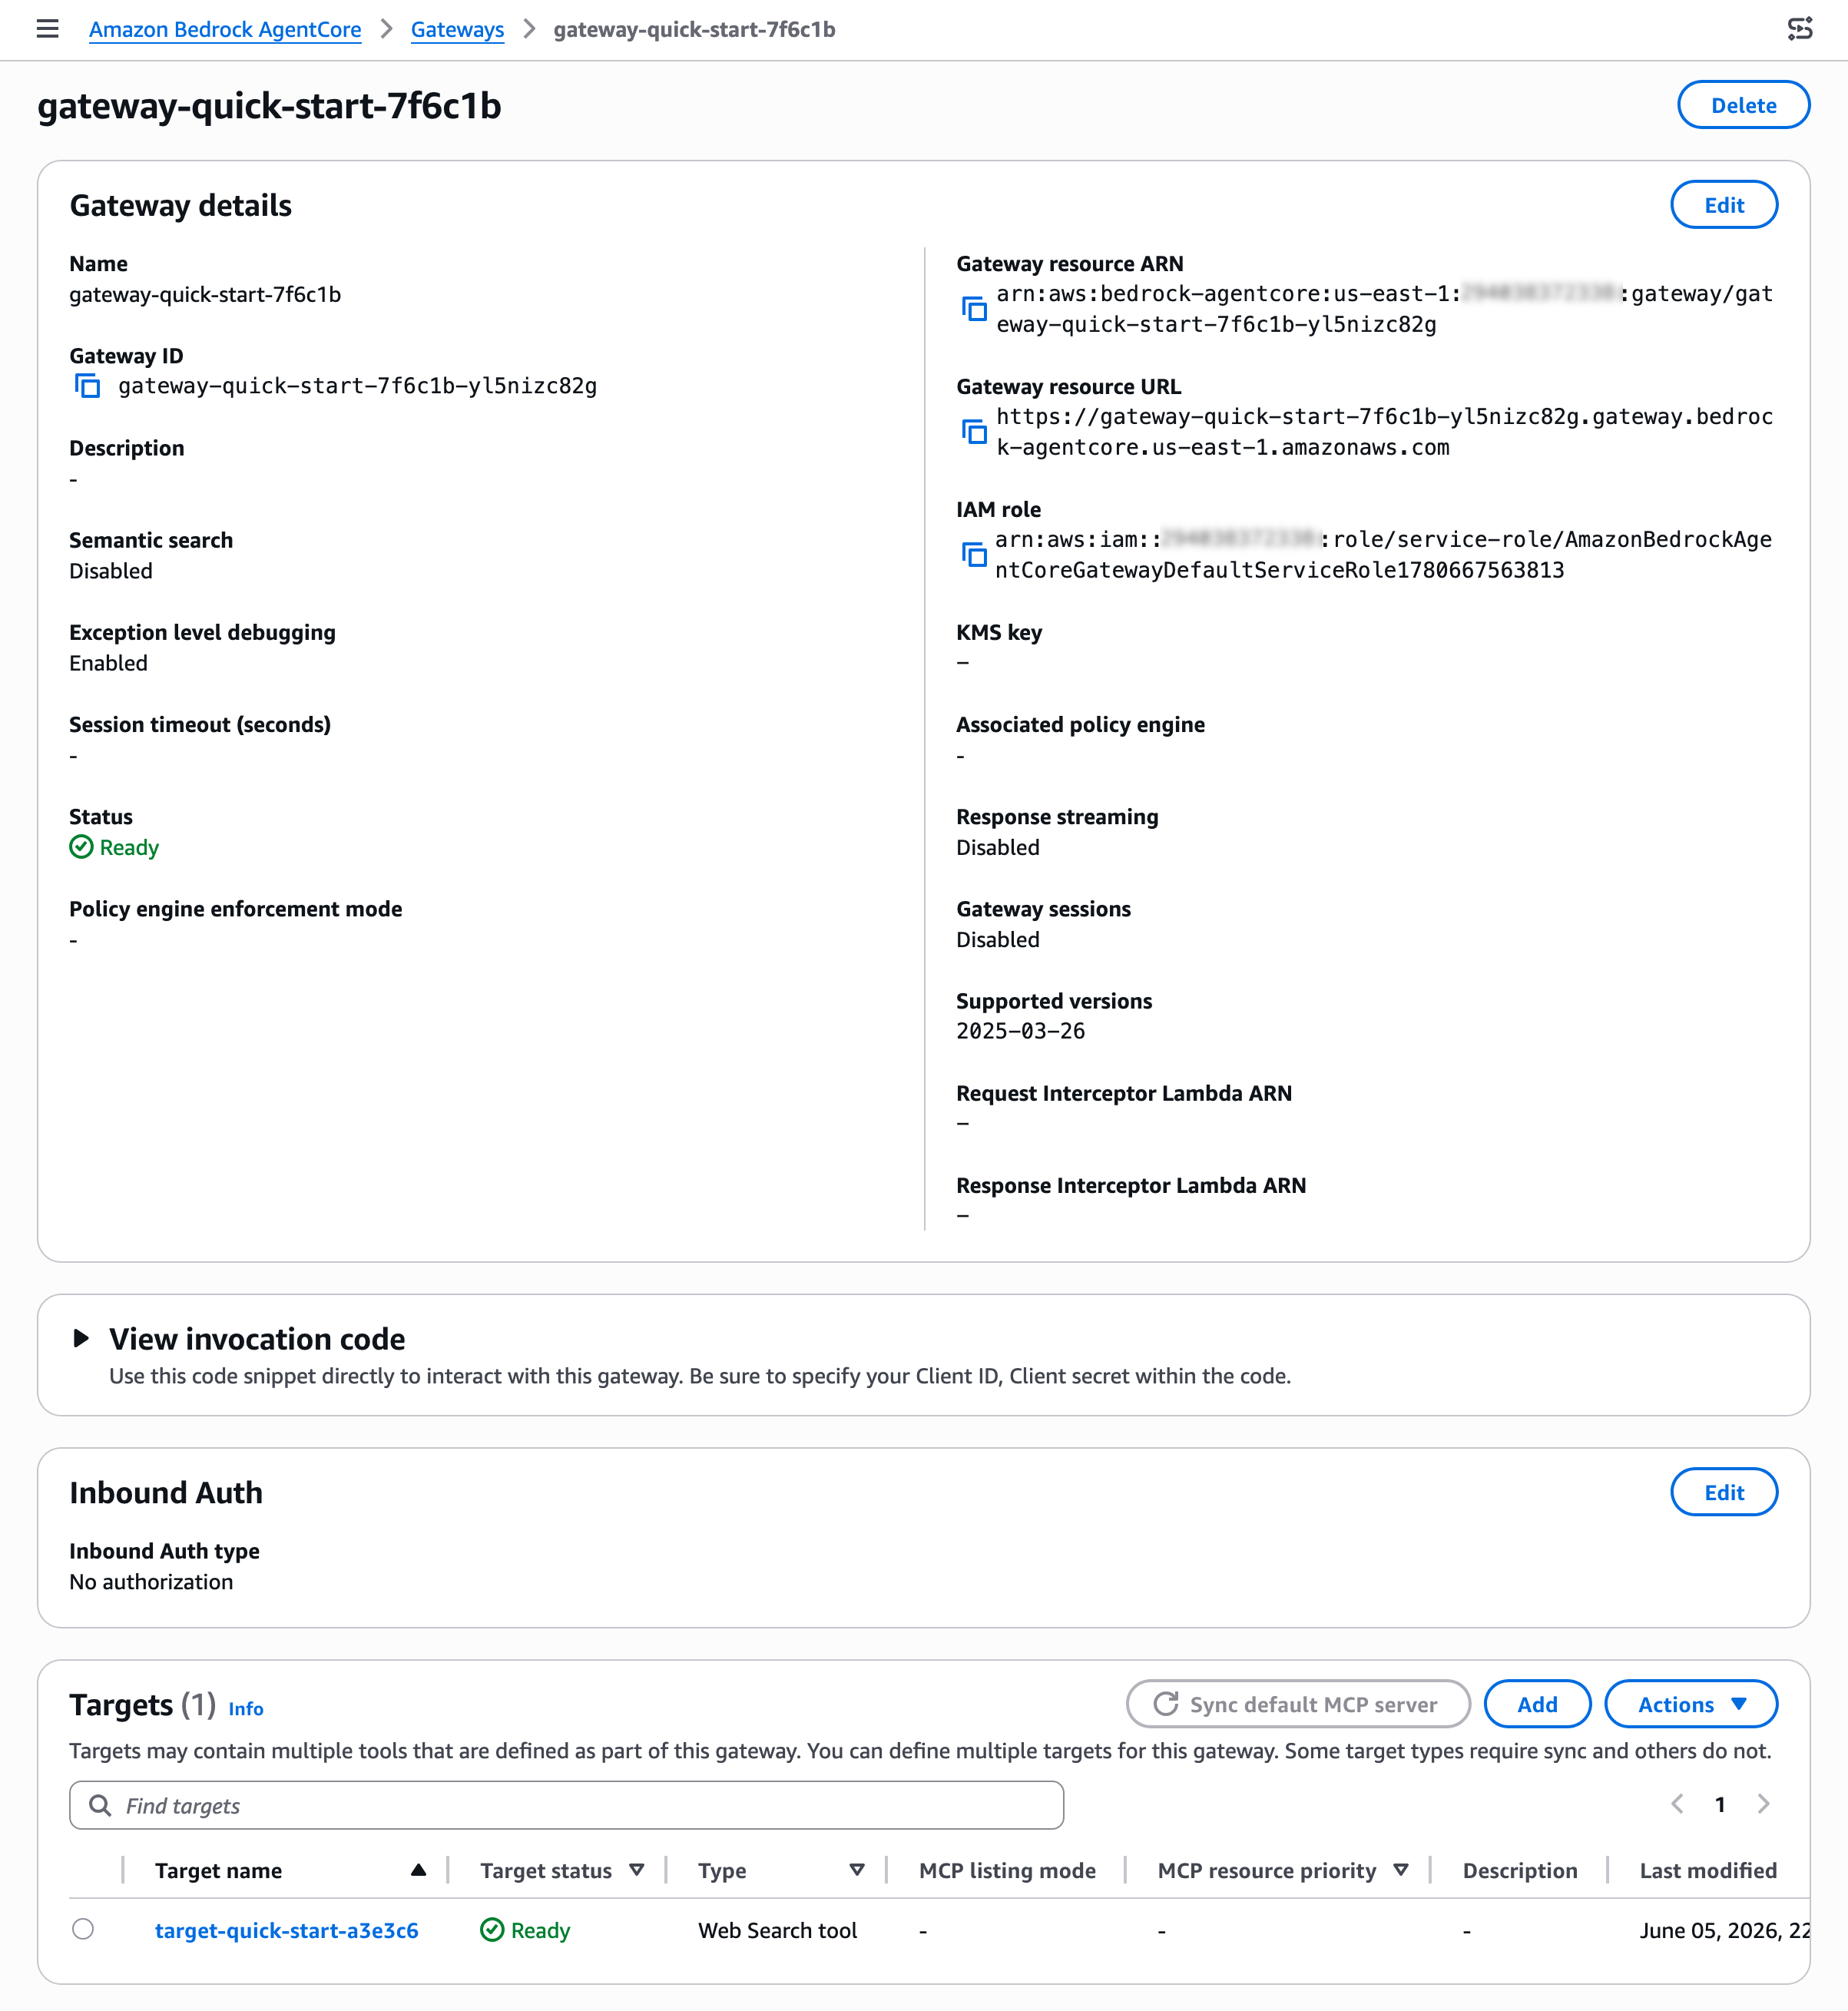
After creating your gateway, you can find the Web Search tool target on the detail page of your gateway. You can also add a new Web Search tool target to an existing gateway.

To interact with Web Search tool, use the sample invocation code in the View invocation code section. You can use code snippets through Python codes with API requests, MCP Python SDK, Strands MCP Client, and MCP Inspector.

For example, you can interact with the MCP Inspector, an interactive developer tool for testing and debugging MCP servers. When you connect to the MCP server through the Gateway resource URL, you will find a Web Search tool for each connector target on the Gateway. Enter input the web search query and choose Run Tool to get the results.

To learn more about how to use Web Search on Bedrock AgentCore, visit the Bedrock AgentCore Gateway documentation.

Customer voices
Some of our customers had early access to this new feature. This is what they shared with us:

Benchling helps scientists accelerate R&D, making it easy to centralize scientific data, collaborate across teams, and access insights. Nicholas Larus-Stone, Head of AI Agents at Benchling shared “Scientists using Benchling AI can now ask about a target they’re actively working on and get answers grounded in both their institutional data in Benchling and published literature. The result is more complete science, and hypothesis generation done right. Because we’re using the Web Search tool on Amazon Bedrock AgentCore, customers have a secure, governed environment to bring that high quality published data into their workflows without compromising how they manage their data.”

Gen Digital leads consumer and small business cyber safety, offering antivirus, antimalware, identity and privacy protection, virtual private networks, and cloud backup. Iskander Sanchez-Rola, Senior Director of AI & Innovation, Gen Digital shared “With the Web Search tool on Amazon Bedrock AgentCore, Norton Revamp helps professionals build their online reputation with current, grounded content ideas shaped by what’s actually happening in the world today. What we value most is that AWS uses its own search index and keep queries within our trusted AWS environment.”

To read more customer stories, visit the Amazon Bedrock Customers.

Now available
Web Search on Amazon Bedrock AgentCore is generally available today in the US East (N. Virginia) Region. For Regional availability and a future roadmap, visit the AWS Capabilities by Region.

You can get started with Web Search on Bedrock AgentCore at no additional cost. You pay only for the data transfer charges you use for the Gateway. New AWS customers also receive up to $200 in Free Tier credits. To learn more, visit the Amazon Bedrock AgentCore pricing page.

Try it in the Amazon Bedrock AgentCore console and send feedback to AWS re:Post for Amazon Bedrock AgentCore or through your usual AWS Support contacts.

Channy

Proactively reduce tech debt autonomously with AWS Transform – continuous modernization (preview)

Post Syndicated from Micah Walter original https://aws.amazon.com/blogs/aws/proactively-reduce-tech-debt-autonomously-with-aws-transform-continuous-modernization-preview/

Today, we’re announcing AWS Transform – continuous modernization (preview), a new capability of AWS Transform for continuous, autonomous tech debt analysis and remediation at scale. AWS Transform already helps enterprises migrate out of data centers, modernize mainframe and Windows applications, and handle the undifferentiated work of software maintenance: upgrading Java versions, swapping deprecated frameworks, and updating AWS Lambda runtimes before they reach end of life. This new experience builds on this. Customers get full visibility into the state of their codebase across thousands of repositories, prioritized findings, and the pull requests that make the fixes.

Engineering organizations typically consume up to 30% of IT budgets. Customers stitch together point tools: one to detect dependency issues, another to flag vulnerabilities, another for code quality. But no existing tool detects, prioritizes, and remediates tech debt continuously and at scale. The result is a manual, app-by-app cycle that drains engineering capacity. Leaders fall back on self-reported team status that lags reality and hides regressions. AI-assisted development makes this worse: as coding agents accelerate the pace of change, tech debt accumulates faster than developers can keep up. Customers need a capability that detects, prioritizes, and remediates tech debt continuously, autonomously, and at scale.

Continuous analysis
To address the visibility challenge, this new capability within AWS Transform automatically scans your code repositories against configurable baselines and generates findings in hours, not weeks. Out of the box, AWS Transform – continuous modernization includes policies for detecting end of life dependencies, deprecated frameworks, and other common sources of technical debt. You can also extend these with your own remediation patterns specific to your organization, including approved libraries, internal coding standards, or tech debt policies your platform team already enforces. For example, if your team has deprecated an internal library or prefers a particular logging pattern, you can codify that as a policy and run it across all your repositories continuously.

Unlike periodic manual efforts, continuous analysis provides ground truth directly from your code. When a repository falls behind your baseline, you know immediately, showing which components are behind and by how much, regardless of how the team chooses to address it. This eliminates the need for status check-ins and manual compliance tracking, giving platform teams an always current view of their technical debt landscape.

Autonomous remediation at scale
Once you’ve identified and prioritized findings, you can configure autonomous remediations that generate pull requests for affected repositories automatically. This new AWS Transform capability provides out-of-the-box remediation transformations for common scenarios such as Java version upgrades, SDK migrations, and library updates. You can also create custom transformations for organization-specific patterns.

When you launch a remediation, the continuous modernization capability creates pull requests for each affected repository, notifying the owning team with a message like: “This repository is behind on your organization’s baseline for this dependency. Here’s a PR that resolves it.” Teams can review and merge the PR, or choose to remediate using their own approach. Either way, continuous analysis detects when the fix is in place, providing ground truth without requiring manual confirmation.

AWS Transform – continuous modernization integrates with AWS Security Agent to detect and remediate security vulnerabilities at the source-code level, so security findings flow into the same prioritized list and pull-request workflow as other tech debt.

Let’s try it out
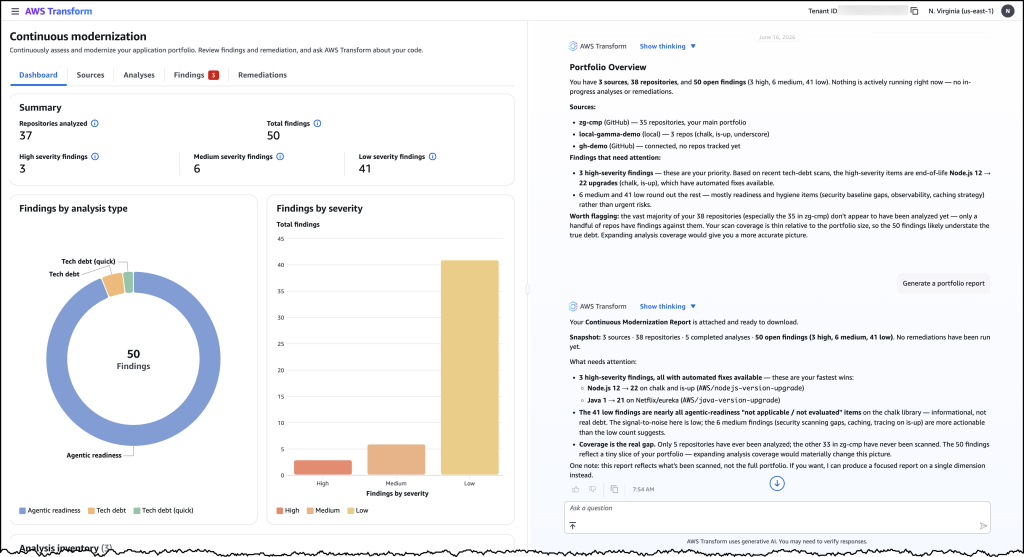
To get started with, I navigated to the AWS Transform web application. From the dashboard, I can see an overview of my organization’s repositories and their current status against my configured baselines.

First, I connected my source control system and initiated an analysis against my specified policies. Within hours, the analysis returned findings across my repositories, showing which ones were behind the baseline and by how much. I could see the severity, the number of affected files, and the specific tech debt patterns detected.

From here, I selected a group of high-priority findings and launched a remediation campaign. AWS Transform – continuous modernization generated pull requests for each affected repository. I could monitor the campaign’s progress in real time, seeing which PRs were created, which were merged, and which repositories returned to compliance.

Image 1: AWS Transform – continuous modernization dashboard showing a portfolio overview of your technical debt findings across all connected repositories.

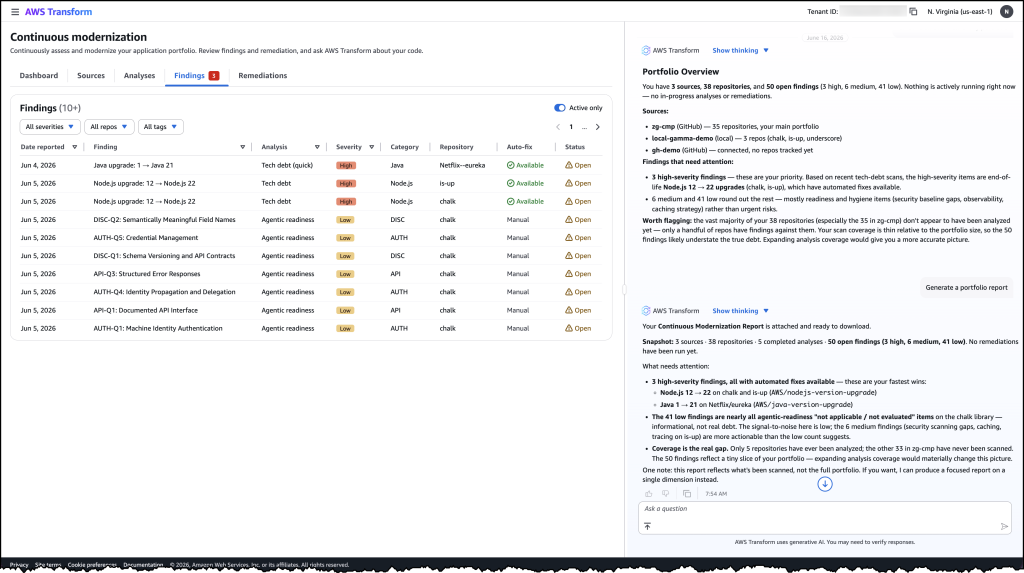
Image 2: The detailed findings view listing individual tech debt items by severity, category, and repository with their available remediation options.

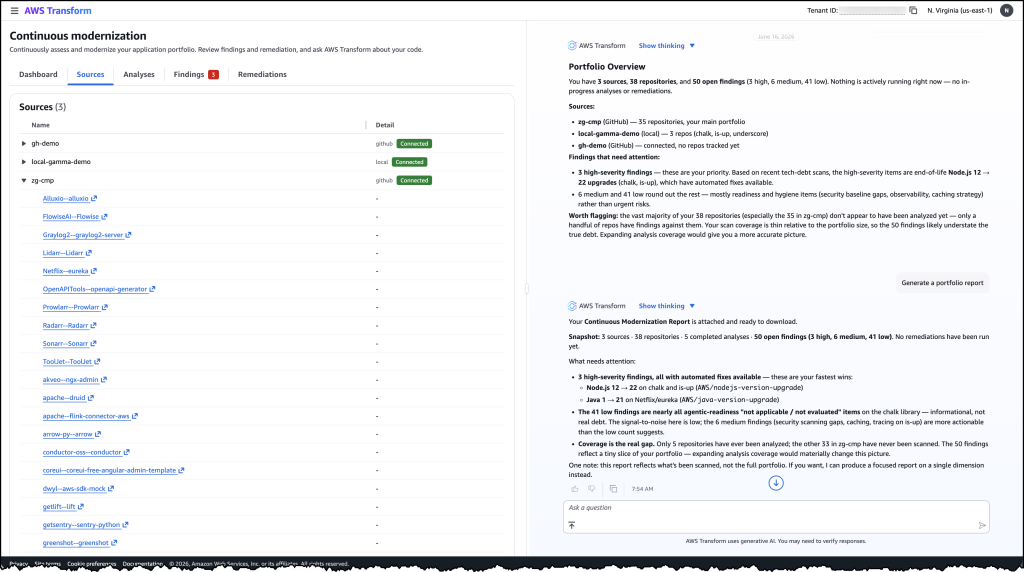
Image 3: The sources view showing connected repositories from GitHub and local environments that continuous modernization is tracking for analysis.

Faster ways to modernize
These capabilities support two distinct approaches to code modernization. In continuous mode, you can use continuous modernization to keep your codebases current as baselines evolve. Think of this as the day-to-day work of upgrading libraries, applying security patches, and enforcing coding standards across your organization.

For larger modernization projects, such as migrating from one framework to another or upgrading a major runtime version across hundreds of applications, you can use campaign mode for targeted, project-based modernization. AWS Transform custom continues to provide the flexible primitive for these larger efforts. AWS Transform – continuous modernization is purpose-built for the recurring, high-volume work that platform teams manage every day.

Now available
AWS Transform – continuous modernization (preview) is available today. You can get started through the AWS Transform web application, via the AWS Transform Kiro Power, or through MCP and skills for integration with your existing coding agents. To learn more, visit the AWS Transform documentation.

AWS Security Agent adds threat modeling, Kiro power and Claude Code plugin, and more

Post Syndicated from Channy Yun (윤석찬) original https://aws.amazon.com/blogs/aws/aws-security-agent-adds-threat-modeling-kiro-power-and-claude-code-plugin-and-more/

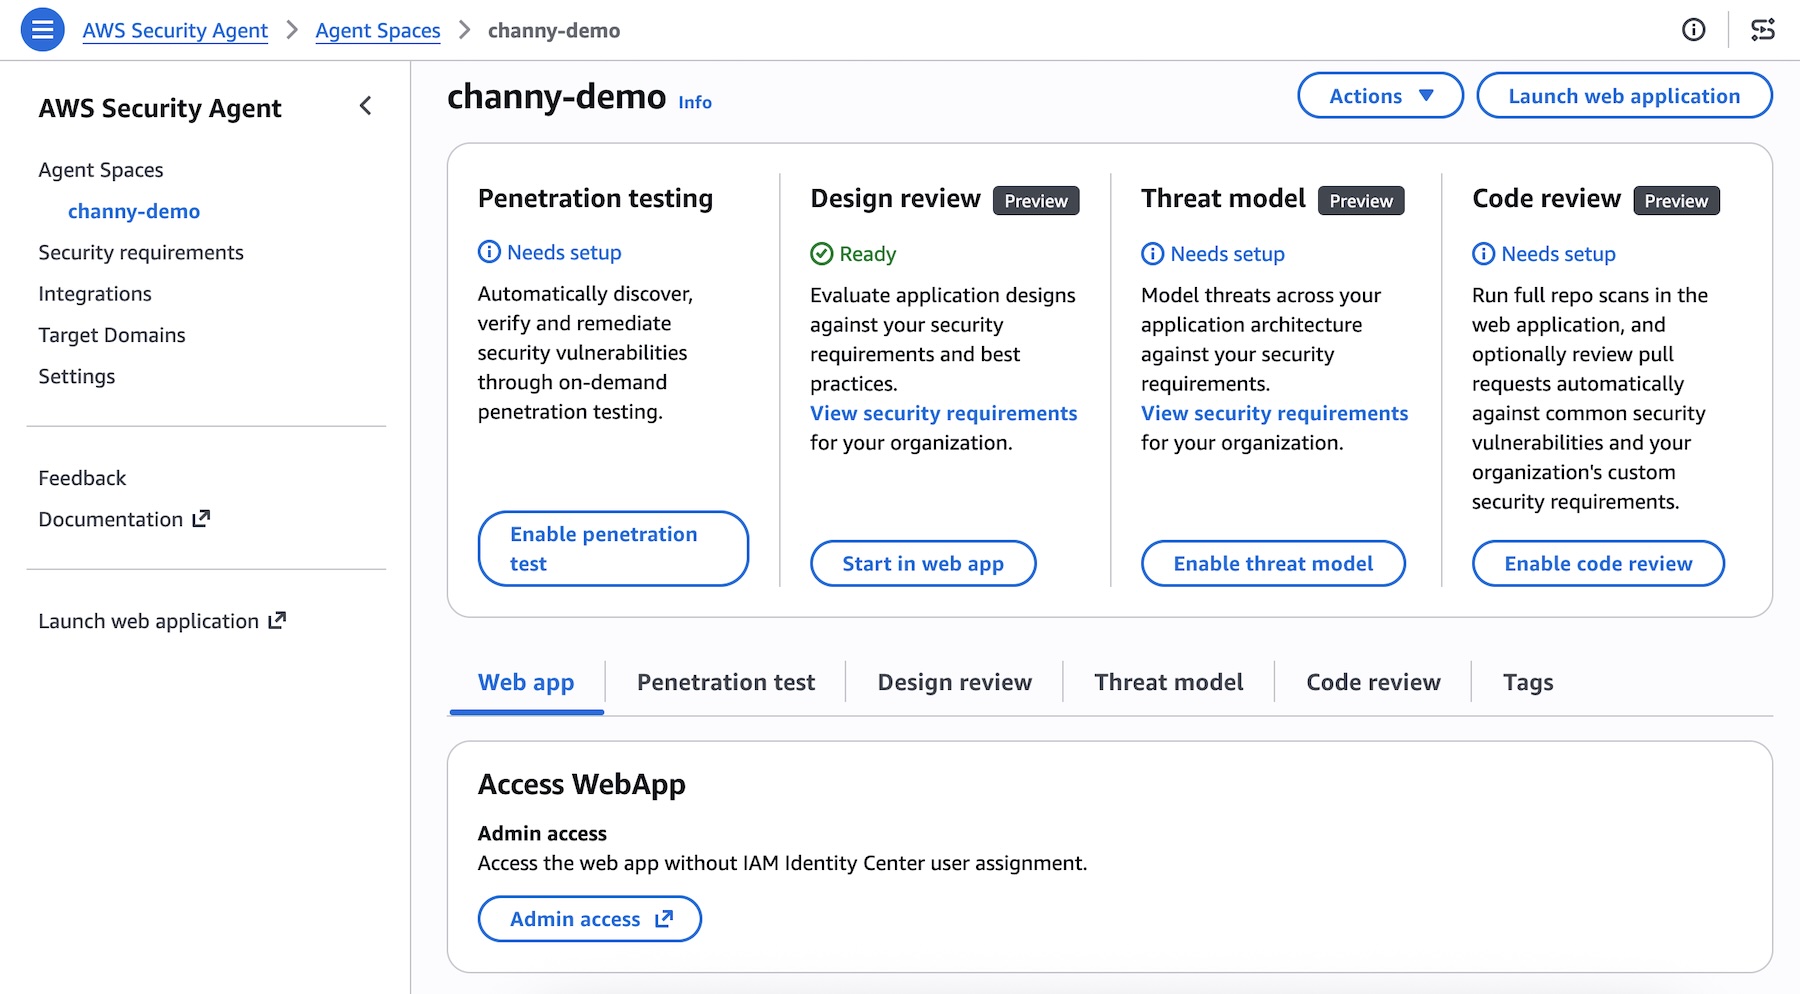
At re:Invent 2025, we previewed AWS Security Agent (now part of AWS Continuum), a frontier agent that proactively secures your applications throughout the development lifecycle across all your environments. You can perform on-demand penetration testing customized to your application, discovering and reporting security risks verified through exploitability testing.

Since the preview, we announced general availability for on-demand penetration testing and the preview of full repository code review that performs deep, context-aware security analysis of your entire codebase.

Today, we’re introducing more features based on customer feedback:

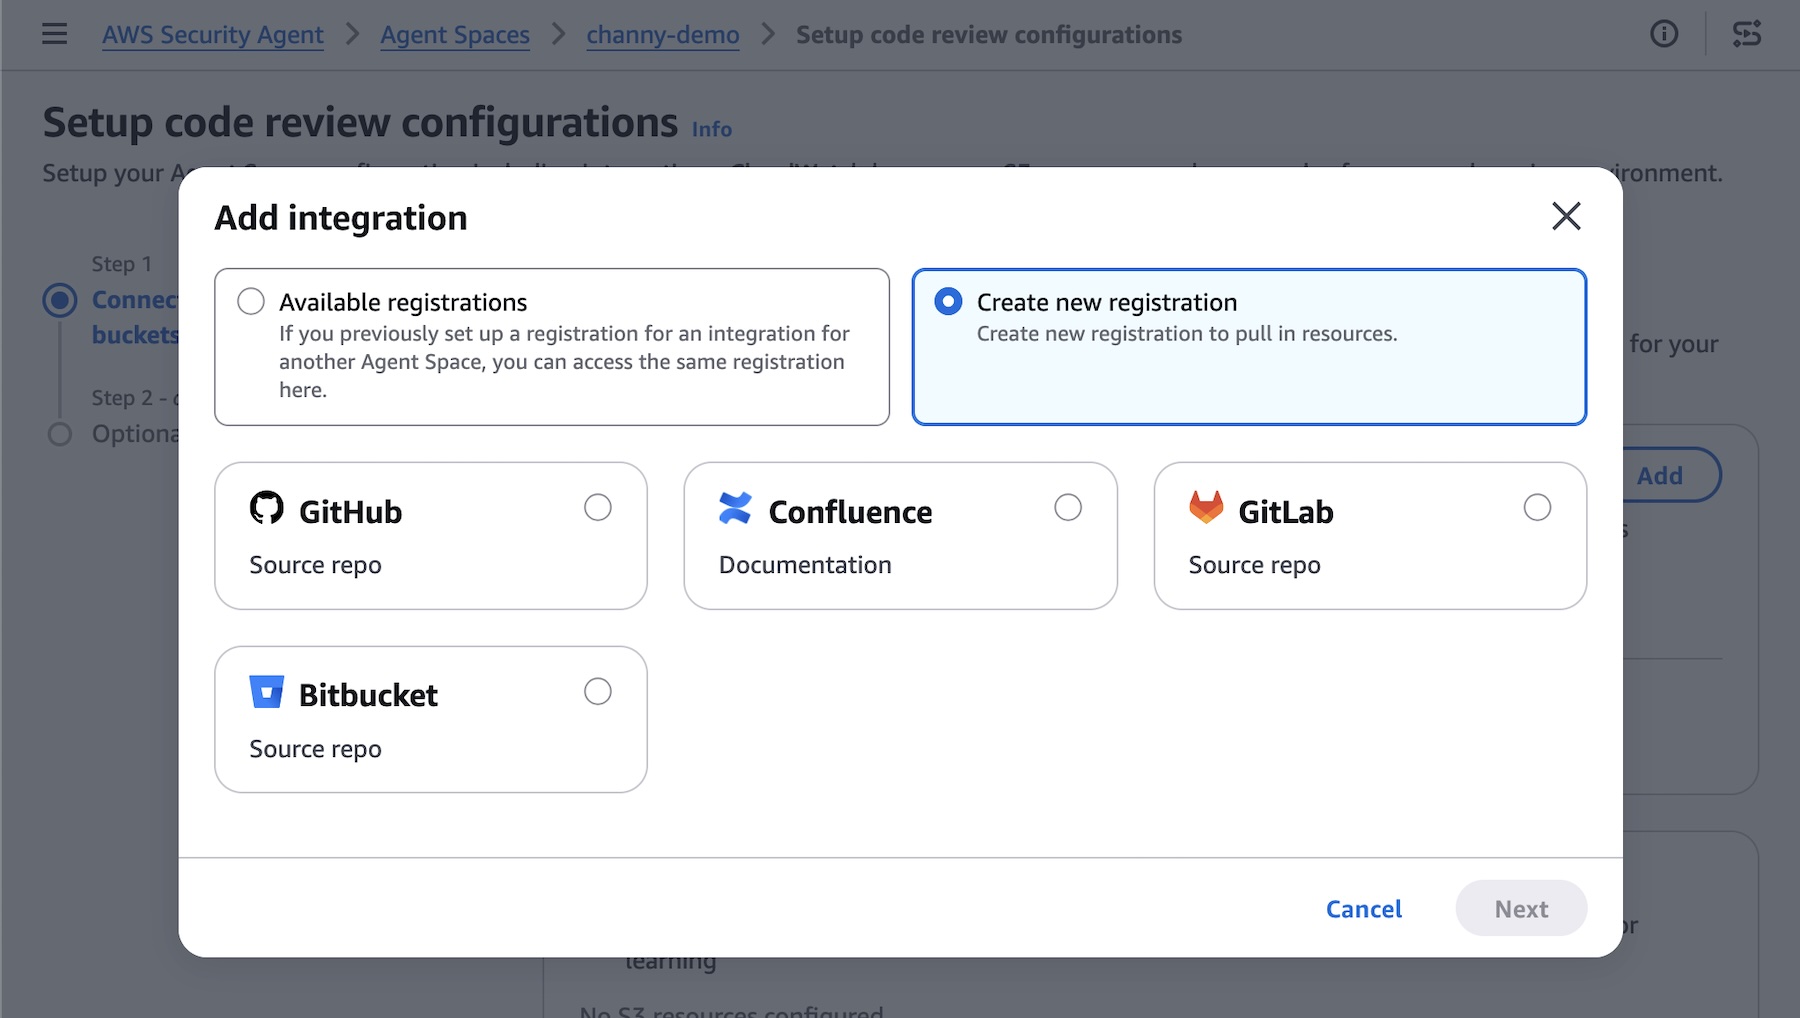
  • Code review updates (Preview) — You can now use pull request scanning with remediation, security requirements packs, and simulated validation. New integrations support GitHub, GitLab, Bitbucket, and Confluence.
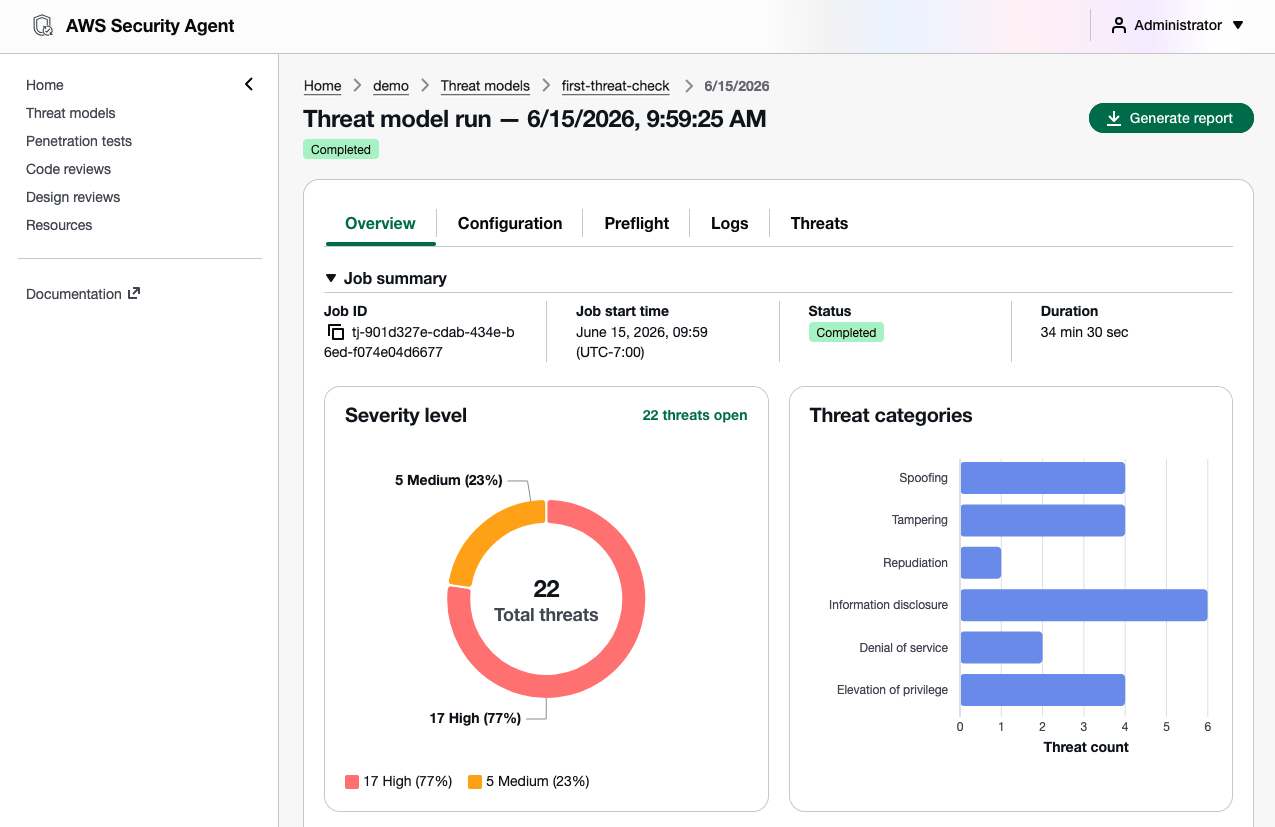
  • Threat modeling (Preview) — AWS Security Agent analyzes your design documents or application source code, understands the full context of your application architecture and identifies threats with recommended mitigations using the STRIDE framework.
  • Kiro power, Claude Code plugin, and MCP integration — You can run code reviews, generate threat models, and remediate findings directly from your IDE, CLI, or any AI-powered IDE through an open MCP integration, with results surfacing inline without any context switching.

Let’s take a closer look at each launch!

Code review updates
You can now connect to GitLab and Bitbucket in addition to GitHub— supporting both SaaS and self-hosted versions, so you can trigger scans regardless of where code lives. You can also integrate Confluence to reference your existing documentation as context for reviews.

To get started, choose Enable code review or update your code review setting in the Security Agent console.

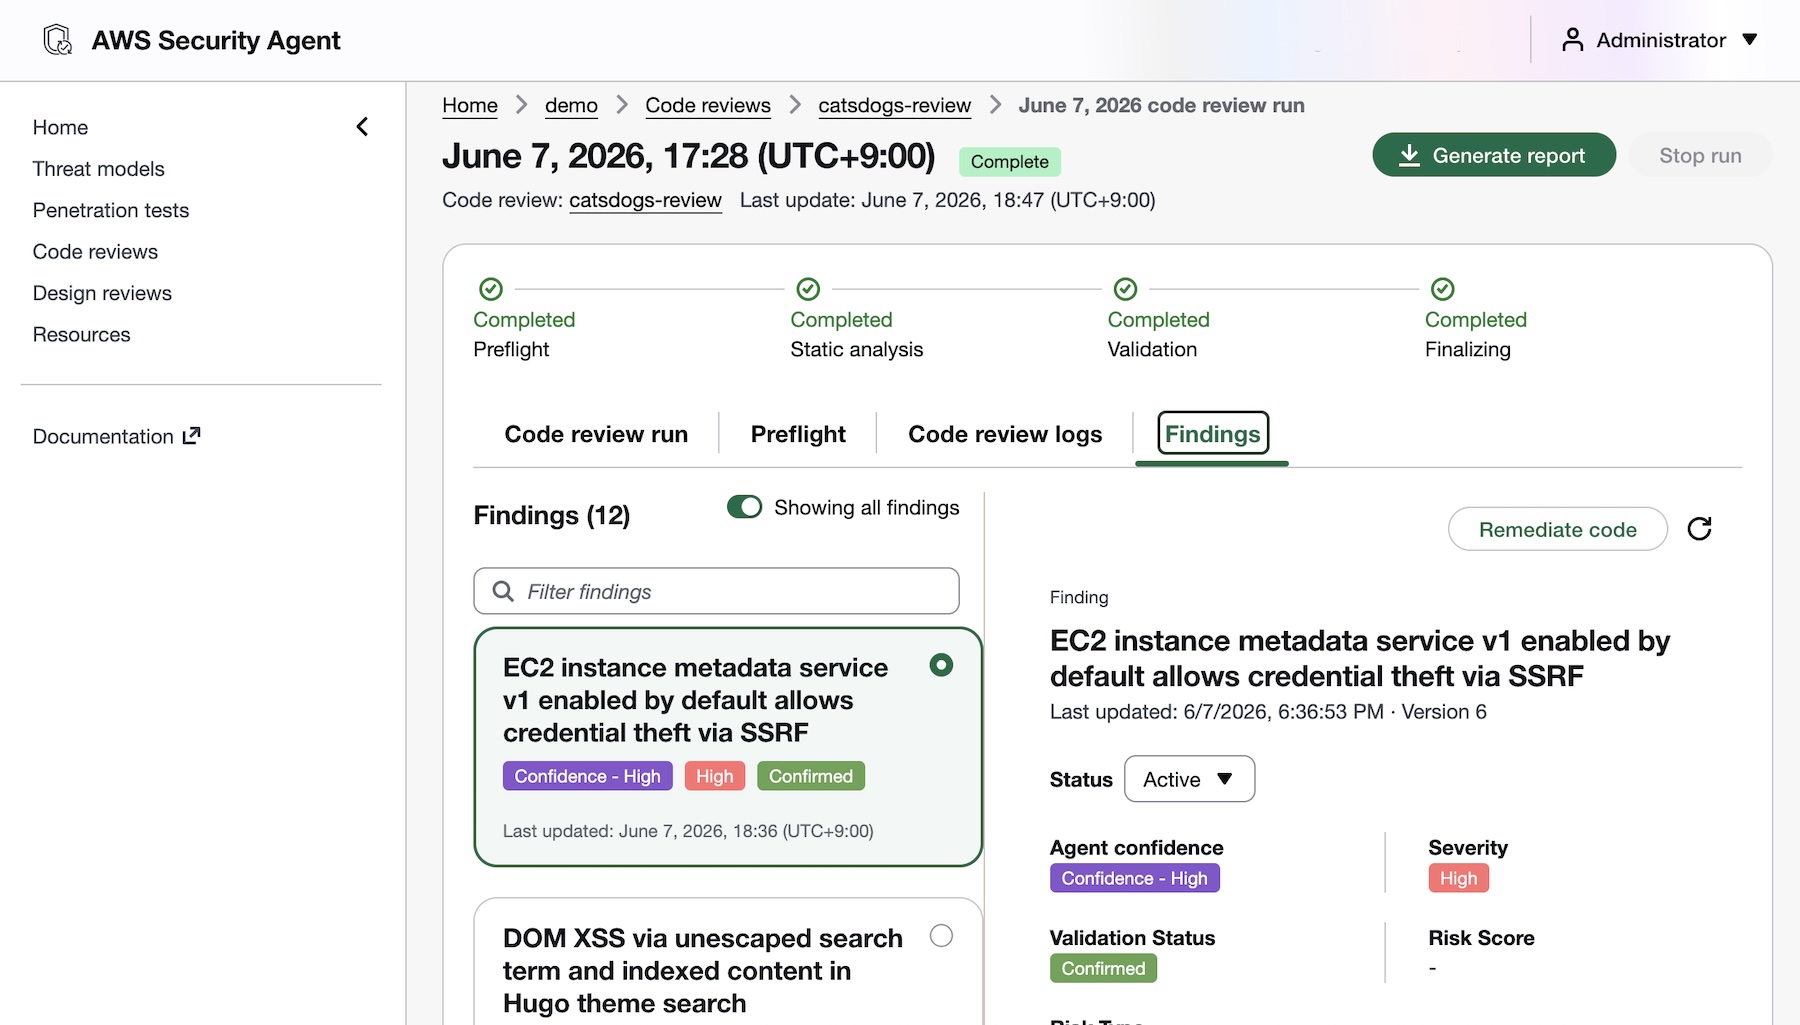
AWS Security Agent introduces deep, reasoning-based analysis on every pull request as well as full repository to identify complex vulnerabilities that go beyond pattern-matching. It checks against your organizational security requirements and common security risks to catch what other tools can’t. To get started, access the Security Agent web application and run your code review.

You’ll receive fix commits and remediation guidance directly in your GitHub, GitLab, or Bitbucket workflow, while your security teams configure the repositories to be monitored and intervene on critical issues. AWS Security Agent validates findings in simulated environments to demonstrate proof of exploitability. This embeds security expertise across all repositories, reducing security-related delays in the development pipeline.

To learn more about new code review features, visit Create a code review in the AWS Security Agent User Guide.

Design review updates
You can continuously validate your security requirements across every design and code review with managed compliance packs: AWS WAF, NIST CSF, PCI DSS, and AWS best practices, or import your own organizational requirements directly from internal documents or Confluence. Every finding maps back to your compliance posture, so teams stay audit-ready as they build.

To learn more, visit the design review documentation.

Threat modeling
AWS Security Agent generates threat models based on your design documentation or code repository, creates and build context about the application, including data flows, architecture, and trust boundaries. It maps out all components of your application, identifies potential threat actors and attack vectors, determines where weaknesses may exist, and prioritizes threats so you know what to address first.

To get started, choose Enable threat model and Connect source code repository in the Security Agent console.

To learn more, visit the threat modeling documentation.

Kiro power and Claude Code plugin for Security Agent
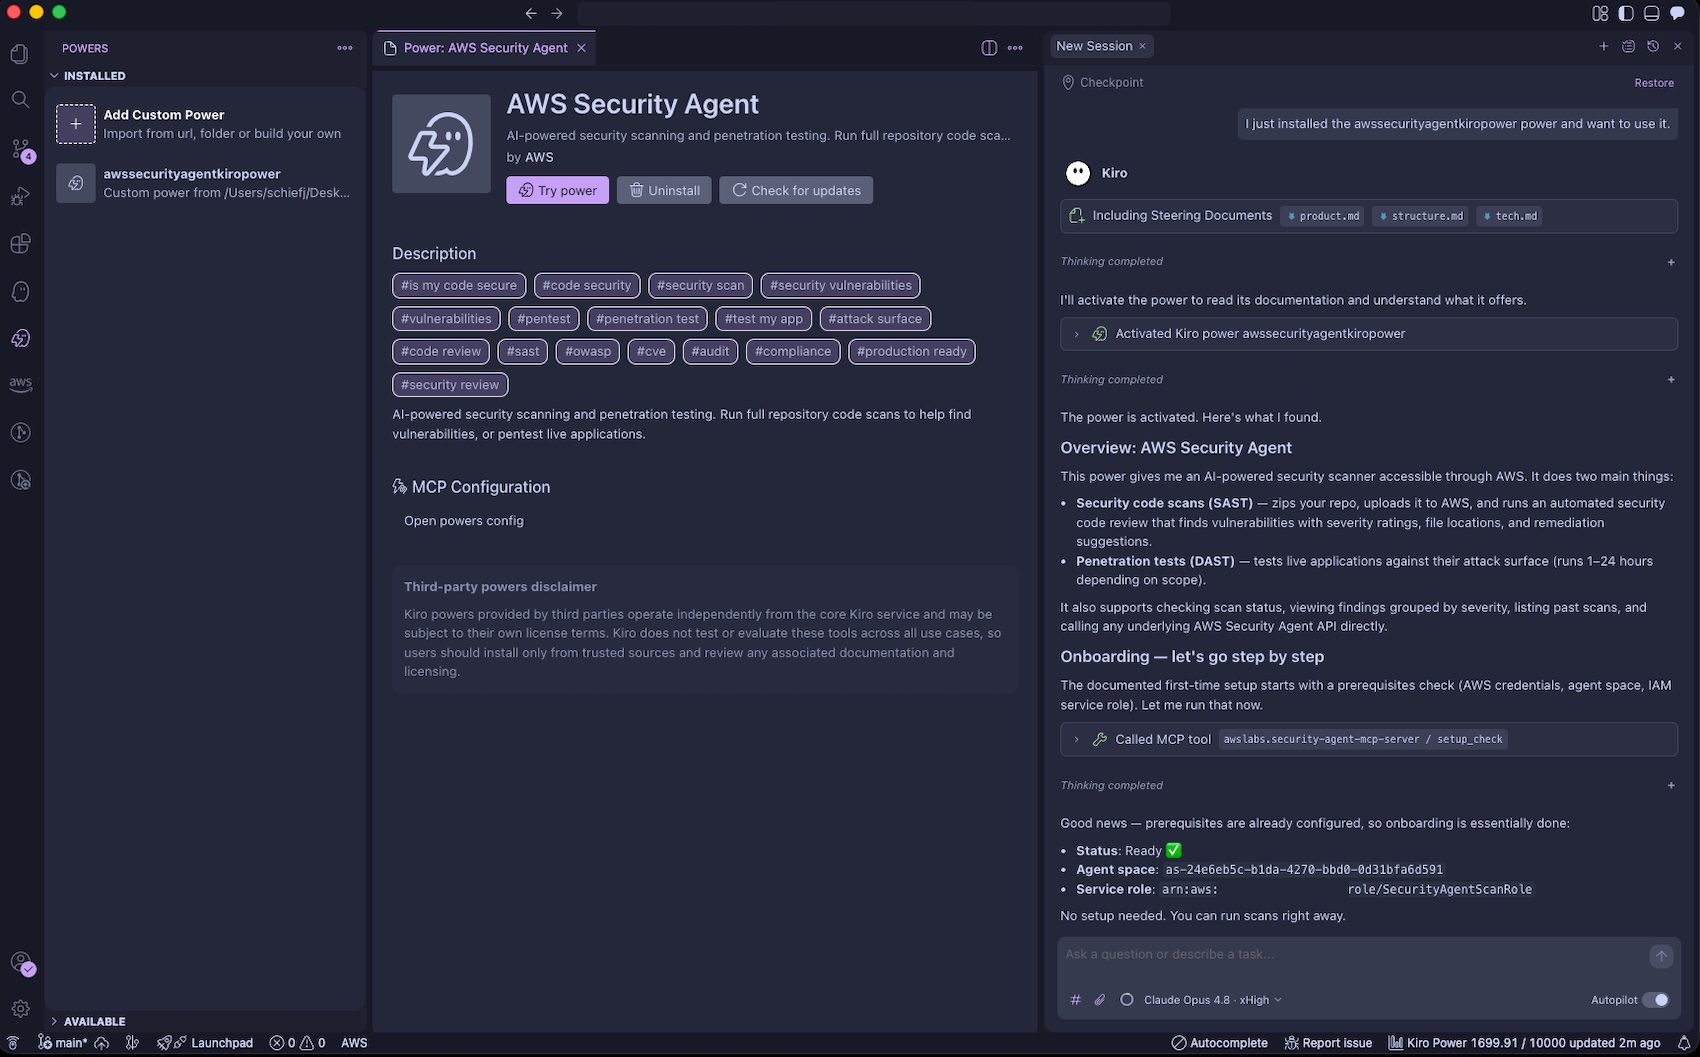
AWS Security Agent introduces a new Kiro power and Claude Code plugin (coming soon) and can be integrated with any AI IDE through an open MCP integration to secure your applications. You can trigger threat models and code reviews directly from your IDE, with results surfacing inline without any context switching.

To get started, install the Kiro power, and run your prompts. The Kiro power uses the AWS Security Agent MCP server. You can get started with the power by asking “Set up AWS Security Agent“. Kiro will check if you have an Agent Space and ask if you would like to use the existing one or create a new one.

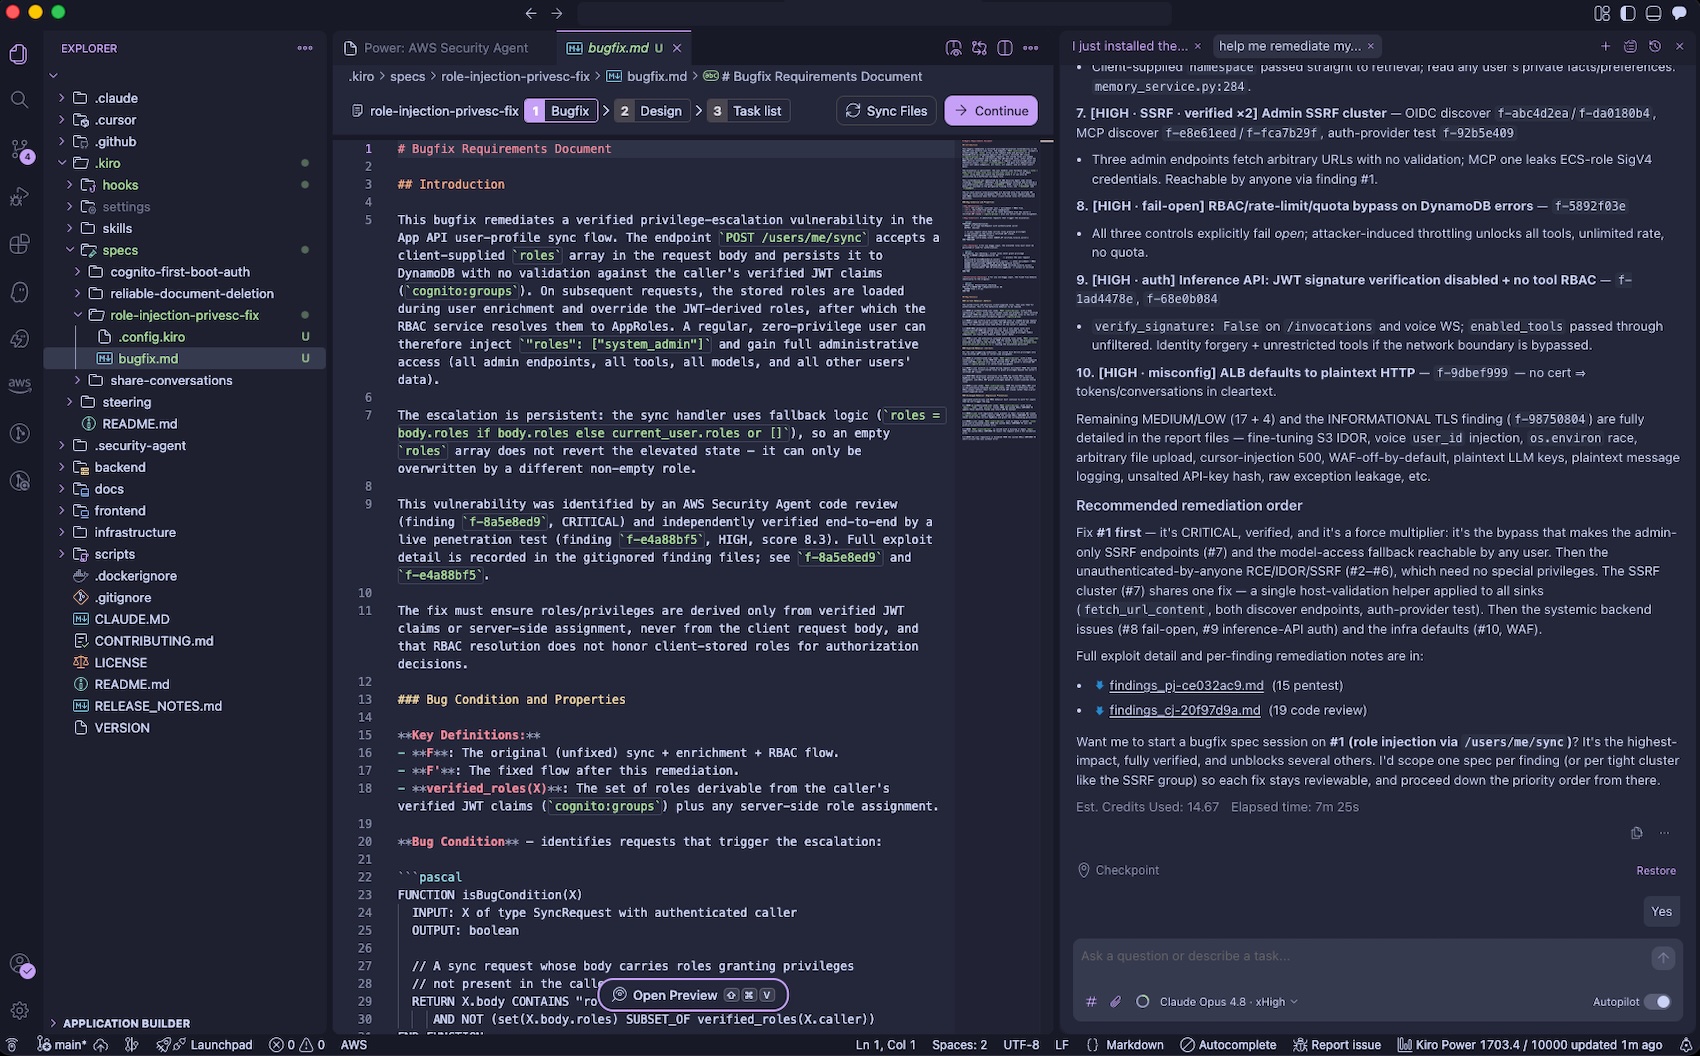
With the Kiro power for Security Agent, you can catch vulnerabilities on every pull request as you build and scan an entire repository to surface accumulated risk by asking “Run a full security scan on this repo“. The Security Agent power includes an Agent hook to evaluate if a code review diff scan should be started after the Kiro agent has completed its turn. Before deploying to production, you can run a penetration test from your CLI to find what most scanners miss. Security Agent closes the loop by validating every finding and generating ready-to-implement code fixes.

You can pull the findings back into your development environment by asking “help me remediate my findings“. The Kiro power for AWS Security Agent will download findings to your local workspace, prioritize the most critical finding, and offer to start a bugfix spec session. You can iterate on fixing the findings using their familiar IDE with their existing tooling, steering, powers, and MCP servers.

You can also run threat models through the Kiro power in the IDE by asking “Build a threat model for this application“. The generated threat model is saved to .security-agent/threat_model.md

To learn more, visit the Kiro power for Security Agent.

Now available
AWS Security Agent understands the full security context across your software development lifecycle by covering design-time security (design reviews and threat modeling in preview), development-time security (code review in preview), and deployment-time security (penetration testing in GA), in a single, unified agentic offering. To learn more, visit the AWS Security Agent product page and the technical documentation.

These features are now available in AWS commercial Regions where AWS Security Agent is available. For Regional availability and the future roadmap, visit the AWS Capabilities by Region. For detailed pricing information and to access our 2-month free trial offer, please visit the AWS Security Agent pricing page.

Give it a try in the Security Agent console and send feedback to AWS re:Post for Security Agent or through your usual AWS Support contacts.

Channy

Amazon S3 annotations: attach rich, queryable context directly to your objects

Post Syndicated from Daniel Abib original https://aws.amazon.com/blogs/aws/amazon-s3-annotations-attach-rich-queryable-context-directly-to-your-objects/

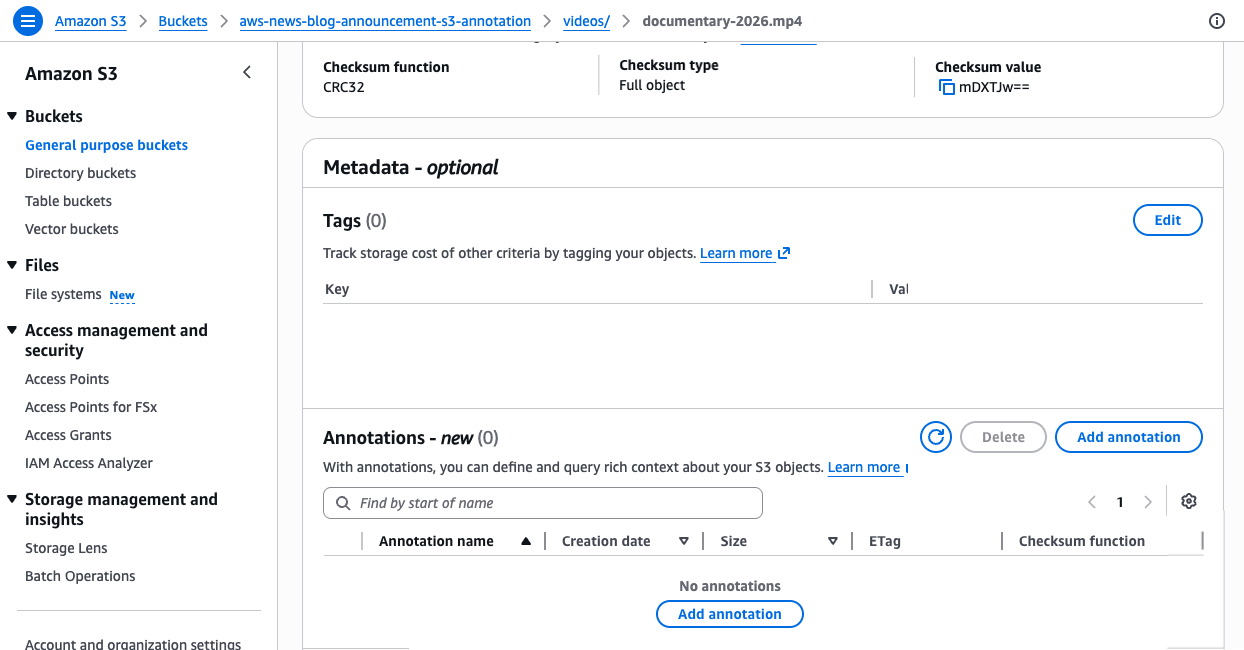
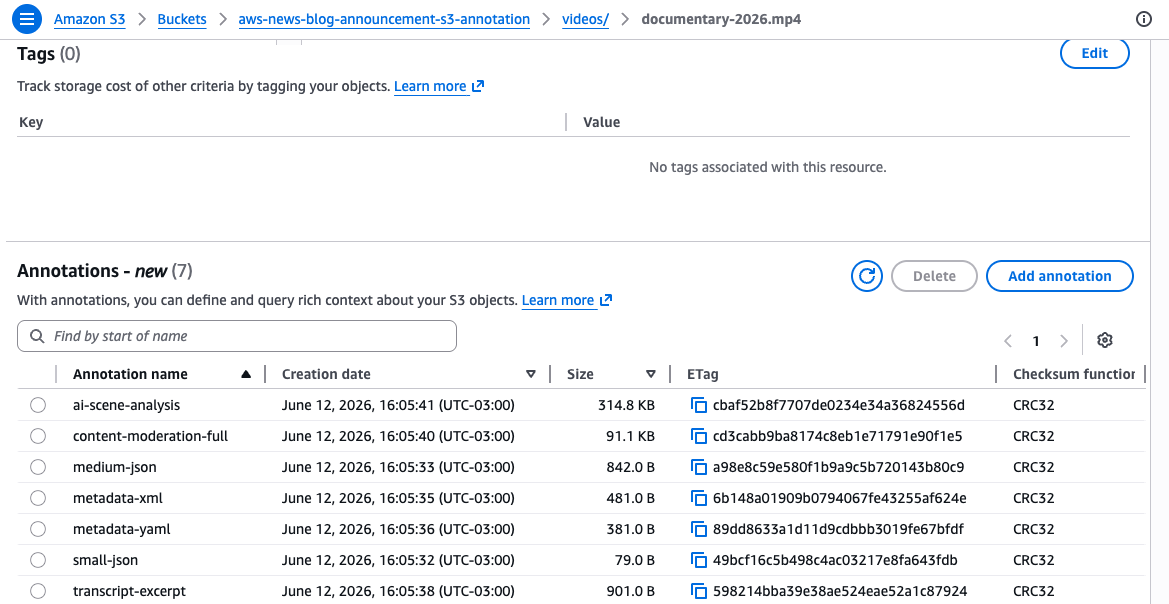
Today, we’re announcing a new metadata capability for Amazon Simple Storage Service (Amazon S3) called annotations, enabling you to attach rich, large-scale business context directly to your objects. You can store up to 1,000 named annotations per object, each up to 1 MB in size, totaling up to 1 GB per object, in flexible formats like JSON, XML, YAML, or plain text. You can modify or delete an annotation at any time, without re-writing your objects, making it easy to keep your object context current.

Organizations are building AI agents and autonomous workflows that need to find, understand, and act on data without human intervention. To support these agentic workflows, you need metadata that can evolve alongside the data, scale to petabytes of objects, and remain queryable without expensive retrieval.

With S3 annotations, you can store context such as AI-generated transcripts, content ratings, or technical specifications directly alongside your objects. Your context moves automatically with the object during copy, replication, and cross-region transfers, and S3 removes it when you delete the object. When you enable S3 Metadata, annotations automatically flow into fully managed annotation tables that you can query with Amazon Athena and other analytics engines.

Common use cases
Annotations solve complex metadata challenges across industries:

  • Media & Entertainment: Track transcripts, content moderation results, subtitle files, and licensing metadata as separate annotations on video assets, eliminating the need to synchronize metadata across multiple media asset management systems.
  • Financial Services: Attach AI-generated investment summaries and sentiment analysis to research documents, enabling autonomous research agents to discover relevant datasets through natural-language queries without maintaining separate metadata databases.
  • Life Sciences: Annotate clinical trial data with regulatory status, patient cohort details, and approval chains, making compliance audits faster while keeping full context accessible for archived data in Amazon S3 Glacier storage classes without retrieval charges.

How annotations address metadata challenges
Amazon S3 already supports several ways to describe your objects. System-defined metadata captures properties like size and storage class. Object tags support operational tasks like access control and lifecycle management. User-defined metadata lets you add small amounts of custom information at upload time.

While these capabilities work well for their intended purposes, they have limitations when you need to attach much richer context without building and maintaining separate metadata systems. Annotations address these needs by providing metadata capabilities at a fundamentally different scale and flexibility, offering mutable, queryable context per object compared to 10 immutable tags or 2 KB of headers.

Capability Max size Mutable? Best for
System-defined metadata Fixed No Object properties (size, storage class, creation time)
User-defined metadata 2 KB No (set at upload) Small custom key-value pairs
Object tags 10 tags, 128/256 characters per key/value Yes Access control, lifecycle rules, cost allocation
Annotations 1 GB (1,000 × 1 MB) Yes Rich business context (JSON, XML, YAML, plain text)

Today, metadata describing S3 objects often lives in separate databases or sidecar files, requiring complex synchronization workflows that can exceed data storage costs. When you enable S3 Metadata annotation tables, this context becomes queryable at scale through Amazon Athena. AI agents can discover your data through natural language with the S3 Tables MCP server, which provides a standardized interface for AI models to query your annotations. You can query annotations for objects in any storage class, without restoring the objects or paying retrieval charges.

Getting started with annotations
To start using annotations, make sure your AWS Identity and Access Management (IAM) policy or bucket policy grants permissions for the s3:PutObjectAnnotation and s3:GetObjectAnnotation actions. You can then add annotations to any existing or new S3 object using the PutObjectAnnotation API.

For example, a media company can attach technical specifications and AI-produced summaries to a video asset using the AWS Command Line Interface (AWS CLI):

# Create a JSON file with technical metadata
cat > mediainfo.json << 'EOF'
{"codec":"H.265","resolution":"3840x2160","audio_tracks":8,"frame_rate":29.97}
EOF

# Attach it as an annotation
aws s3api put-object-annotation \
  --bucket my-media-bucket \
  --key videos/documentary-2026.mp4 \
  --annotation-name mediainfo \
  --annotation-payload ./mediainfo.json
# Attach a plain-text AI-generated summary as a separate annotation
echo "A 90-minute nature documentary covering wildlife migration patterns across three continents, featuring aerial footage and underwater sequences. Languages: English, Spanish, Portuguese." > ai_summary.txt

aws s3api put-object-annotation \
  --bucket my-media-bucket \
  --key videos/documentary-2026.mp4 \
  --annotation-name ai_summary \
  --annotation-payload ./ai_summary.txt

These commands attach two separate annotations to the same video object. The mediainfo annotation stores structured technical specifications as JSON, while the ai_summary annotation stores a text description. Each annotation is identified by a unique name, and you can read and modify each one independently. With unique names for each annotation, you can use different annotations to support multiple concurrent enrichment workflows, for example, one team adding technical metadata while another team adds content classifications, without interfering with each other.

Retrieve a specific annotation using the GetObjectAnnotation API:

aws s3api get-object-annotation \
  --bucket my-media-bucket \
  --key videos/documentary-2026.mp4 \
  --annotation-name mediainfo \
  ./mediainfo-output.json

To see all annotations attached to an object, use the ListObjectAnnotations API:

aws s3api list-object-annotations \
  --bucket my-media-bucket \
  --key videos/documentary-2026.mp4

When you no longer need a specific annotation, remove it using the DeleteObjectAnnotation API:

aws s3api delete-object-annotation \
  --bucket my-media-bucket \
  --key videos/documentary-2026.mp4 \
  --annotation-name mediainfo

You can update an existing annotation at any time by calling PutObjectAnnotation again with the same annotation name. For large objects uploaded using multipart upload, attach annotations after completing the multipart upload using the PutObjectAnnotation API.

Querying annotations at scale with S3 Metadata tables
Attaching annotations to individual objects is useful, but the real power comes when you query across all your annotations at scale. When you enable S3 Metadata annotation tables on your bucket, S3 automatically indexes your annotations into a fully managed Apache Iceberg table, called an annotation table. You can query annotation tables with Amazon Athena or any Iceberg-compatible engine.

To enable annotation tables, use the S3 console or the CreateBucketMetadataConfiguration API. The following example creates a new metadata configuration with annotation tables enabled while keeping journal tables for change tracking and disabling the live inventory table:

{
  "JournalTableConfiguration": {
    "RecordExpiration": { "Expiration": "DISABLED" }
  },
  "InventoryTableConfiguration": { "ConfigurationState": "DISABLED" },
  "AnnotationTableConfiguration": {
    "ConfigurationState": "ENABLED",
    "Role": "arn:aws:iam::123456789012:role/S3MetadataAnnotationRole"
  }
}

This configuration tells S3 to automatically capture all your annotations in a queryable table. Once applied, any annotation you attach to objects in this bucket will appear in the table within approximately one hour.

If the bucket already has a metadata configuration, use the UpdateBucketMetadataAnnotationTableConfiguration API:

aws s3api update-bucket-metadata-annotation-table-configuration \
  --bucket my-media-bucket \
  --annotation-table-configuration '{"ConfigurationState":"ENABLED","Role":"arn:aws:iam::123456789012:role/S3MetadataAnnotationRole"}'

Once enabled, your annotations automatically flow into the annotation table. Journal tables update in near real time, while annotation tables refresh within an hour. Unlike traditional metadata tables that require predefined schemas, annotation tables automatically adapt to any JSON, XML, or YAML structure you write. Each annotation becomes a row in the table with its content stored in a text_value column, letting you query across all annotations without schema migrations.

If you enable annotation tables on a bucket that already has annotated objects, S3 automatically backfills existing annotations into the table. The backfill process runs in the background and can take several hours to days depending on the number of objects.

For example, to find all video assets with more than 8 audio tracks across your entire bucket using Amazon Athena:

SELECT DISTINCT bucket, object_key
FROM "s3tablescatalog/aws-s3"."b_my_media_bucket"."annotation"
WHERE name = 'mediainfo'
AND CAST(json_extract_scalar(text_value, '$.audio_tracks') AS INTEGER) > 8

This query scans the annotation table for all annotations named mediainfo, extracts the audio_tracks field from the JSON content, and returns objects where the count exceeds 8.

Or to find all objects that received new annotations in the last 24 hours through the journal table:

SELECT bucket, key, version_id, record_timestamp, annotation.name
FROM "s3tablescatalog/aws-s3"."b_my_media_bucket"."journal"
WHERE record_timestamp >= (current_date - interval '1' day)
AND annotation.name IS NOT NULL
AND record_type IN ('CREATE_ANNOTATION', 'DELETE_ANNOTATION')

This query uses the journal table to track annotation changes in near real time, which is ideal for building event-driven workflows that respond to new or deleted annotations.

You can also use natural language to search objects by their annotations using agents in Amazon SageMaker Unified Studio or any IDE with the S3 Tables MCP server. For example, asking “find all PG-rated movies with Spanish subtitles from 2023” returns results in seconds instead of the hours it would take querying multiple disconnected systems.

Get started today
You can start using Amazon S3 annotations today in all AWS Regions, including the AWS China Regions. Annotation tables are available in all AWS Regions where S3 Metadata is available.

Whether you’re building AI agents that need to discover data autonomously, managing petabytes of media assets with complex metadata, or tracking compliance context for archived datasets, annotations give you the scale and flexibility to attach rich metadata directly to your objects without managing separate systems.

Annotation storage is always billed at S3 Standard rates, even if the parent object is in S3 Glacier or another storage class. For full pricing details, visit the Amazon S3 pricing page.

To learn more and get started, visit the Amazon S3 Metadata overview page and the Amazon S3 documentation. Send feedback to AWS re:Post for S3 or through your usual AWS Support contacts.

Daniel Abib
DORA Compliance Success Story: How PayNovus Strengthened Operational Resilience with Nebosystems & SecureVisio | InfoSec SEE 2026

Post Syndicated from Dora original https://nebosystems.eu/dora-compliance-with-securevisio-a-nebosystems-success-story/

The Digital Operational Resilience Act (DORA – Regulation EU 2022/2554) has introduced new requirements for financial entities across the European Union, placing operational resilience at the center of cybersecurity and risk management.

At InfoSec SEE 2026, Nebosystems and PayNovus presented a practical case study demonstrating how a financial institution approached DORA readiness through SecureVisio and Nebosystems’ SOC services.

Presented jointly by Nebosystems and PayNovus at InfoSec SEE 2026.

Watch the full conference presentation now:

The Challenge: Meeting the Requirements of DORA

DORA establishes a comprehensive framework designed to strengthen the resilience of financial institutions against cyber threats, technology disruptions and operational incidents.

Among the key areas addressed by the regulation are:

  • ICT risk management;
  • ICT incident management, classification and reporting;
  • Digital operational resilience testing;
  • Third-party ICT risk management;
  • Continuous monitoring and information sharing.

Meeting these requirements often involves multiple stakeholders, complex processes and numerous security tools. Organizations must maintain visibility across their infrastructure, ensure regulatory alignment and establish efficient mechanisms for managing risks and responding to incidents.

For institutions operating in a highly regulated environment, achieving these objectives requires both technological capabilities and specialized expertise.

Nebosystems’ Approach

As a cybersecurity and compliance partner, Nebosystems supports organizations throughout their digital resilience journey by combining consulting expertise, managed security services, regulatory guidance and advanced cybersecurity technologies.

In the PayNovus project, Nebosystems followed a structured implementation methodology designed to align operational practices and technology capabilities with DORA requirements.

The engagement included three major phases:

1. Assessment and Gap Analysis

The project began with a comprehensive assessment of ICT assets, cybersecurity risks and existing operational processes.

Nebosystems worked closely with stakeholders to:

  • Inventory critical ICT assets;
  • Evaluate cybersecurity risks;
  • Perform a gap analysis against DORA requirements;
  • Map regulatory obligations to operational controls;
  • Establish implementation priorities.

This phase created the foundation for a structured compliance and resilience program.

2. SecureVisio Implementation

To support operational and regulatory requirements, Nebosystems implemented SecureVisio, an integrated cybersecurity orchestration platform designed to unify critical security and compliance functions.

SecureVisio provides a centralized environment that combines:

  • Asset management and CMDB capabilities;
  • IT Governance, Risk, and Compliance (GRC);
  • Threat and Vulnerability Management (TVM);
  • Security Information and Event Management (SIEM);
  • User and Entity Behavior Analytics (UEBA);
  • Extended Detection and Response (XDR);
  • Security Orchestration, Automation and Response (SOAR).

By consolidating these capabilities into a single platform, organizations gain improved visibility across their security ecosystem while reducing operational complexity.

During implementation, Nebosystems supported the deployment of centralized security management processes, automation workflows, risk registers and governance procedures necessary for ongoing compliance activities.

3. Continuous Monitoring and Operational Support

DORA requires continuous visibility and resilience capabilities. Nebosystems complements SecureVisio with managed SOC services, providing continuous monitoring, threat detection, incident response support and expert guidance. This helps organizations maintain an active security posture while supporting ongoing compliance efforts.

Business Outcomes

Organizations implementing SecureVisio together with Nebosystems’ SOC services can benefit from:

  • Improved visibility across ICT assets, risks and compliance activities;
  • Faster detection and response to security incidents;
  • Reduced operational complexity through platform consolidation;
  • Lower total cost of ownership compared to multiple standalone tools;
  • Ongoing access to cybersecurity and compliance expertise;
  • Enhanced readiness for evolving regulatory requirements.

Building Operational Resilience for the Future

The PayNovus case study presented at InfoSec SEE 2026 demonstrates how integrated technology, cybersecurity expertise and continuous monitoring can help financial institutions address DORA requirements while strengthening operational resilience. Through SecureVisio and Nebosystems’ SOC services, organizations gain a practical foundation for ICT risk management, incident response, resilience testing and ongoing compliance activities.

If your organization is preparing for DORA compliance, looking to enhance digital operational resilience, or seeking expert support for cybersecurity governance and security operations, Nebosystems can help.

Contact our team to learn more about:

  • Security Operations Center (SOC) services;
  • SecureVisio implementation and integration;
  • Cybersecurity consulting and managed security services.

Discover how Nebosystems can help your organization navigate DORA requirements, strengthen cyber resilience and build a sustainable framework for digital operational resilience.

A Day in the Life of an MDR Analyst: Inside the Modern SOC

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/it-day-in-the-life-mdr-analyst-inside-the-modern-soc

What actually happens inside a SOC when an incident unfolds? Most teams see the alerts and the outcomes, but the decision-making in between is often less visible.

At the Rapid7 2026 Global Cybersecurity Summit, the signature session Inside the Modern SOC: Who Carries You Through an Incident takes a different approach. Rather than focusing on tools or dashboards, it follows a real-world incident from the perspective of the people responsible for investigating and containing it.

The session walks through how modern MDR teams operate under pressure, drawing on real experience across cloud, identity, and on-prem environments. Led by Karl Lankford, Senior Director, Sales Engineering, Rapid7, the discussion brings in perspectives from across the SOC, including incident response and detection, to show how teams work together when it matters most.

Structured around a full incident lifecycle, the walkthrough begins with the initial signal and moves through triage and investigation, following the decisions that shape the outcome. The focus is not on theory but on how incidents are handled in practice, from background and context through to the final result.

What stands out is how much of the process depends on judgment. Alerts are only the starting point. From there, analysts are working to understand context, assess risk, and decide what matters most in the moment. This includes identifying compromised identities, understanding how attackers move across environments, and coordinating response across multiple systems.

The session also highlights how quickly these decisions need to be made. As shown in the high-level timeline, attackers can move from initial access to broader compromise across cloud and on-prem systems in a matter of minutes, which leaves little room for hesitation or uncertainty.

Throughout the walkthrough, the focus stays on what carries organizations through an incident. Detection plays a role, but outcomes are shaped by coordination, tradeoffs, and the ability to act with clarity under pressure. The session also explores how visibility across environments, combined with human-led response, helps teams connect signals and act before impact occurs.

For practitioners, SOC leaders, and teams evaluating MDR, this session offers a grounded view of how modern incident response works under real conditions. It shows what happens between the alert and the outcome, and why that gap is where the real value lies. Watch the full session to follow the investigation step by step and see how MDR teams carry organizations through real incidents.

How Security Leaders Cut Through Complexity to Drive Better Outcomes

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/it-security-leaders-cut-through-complexity-driving-stronger-outcomes-webinar

Security leaders are operating in an environment that is only getting more complex. Expanding attack surfaces, rapid AI adoption, growing toolsets, and increasing pressure to respond faster have made it harder to maintain a clear view of risk and priorities.

At the Rapid7 Global Cybersecurity Summit, the customer panel How Clarity Beats Complexity explores how leaders are navigating that reality in practice. Drawing on perspectives from CISOs and technology leaders across industries, the session focuses on how teams are managing complexity without losing sight of what matters.

Rather than focusing on theory, the discussion is structured around a set of practical questions that reflect what teams are dealing with today. These include where complexity is making security harder to manage, how alerts, data, and handoffs are slowing decisions, and what can look like progress but fails to deliver meaningful outcomes.

As the conversation develops, speakers such as Debby Briggs, VP-CISO at Netscout Systems and Raheem Daya CTO at Target RWE share how their teams are rethinking processes, habits, and assumptions that add noise without improving security. The emphasis shifts toward questioning metrics that measure activity rather than risk, and focusing instead on what drives meaningful outcomes.

From there, the session looks at what is actually making a difference. Topics include how leaders are clarifying priorities, aligning security actions with real business impact, and where visibility and context are proving more valuable than volume. Will Lambert, Information Security Manager at Culligan International adds a practitioner perspective, highlighting how clearer ownership and better coordination across teams help reduce friction in day-to-day operations.

Throughout the session, the focus remains on practical decision-making. This includes managing complexity without oversimplifying, validating investments in areas such as MDR and consolidation, and ensuring security teams are focused on outcomes that improve resilience.

For CISOs, security operations leaders, and teams evaluating their current approach, this panel offers a grounded view of how others are tackling the same challenges.

Watch the full customer panel to hear how security leaders are cutting through complexity and focusing on what actually improves outcomes.

Rapid7’s 2026 Global Cybersecurity Summit: Key Takeaways for Security Leaders

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/it-2026-global-cybersecurity-summit-key-takeaways-security-leaders

Security teams are working in an environment where speed, scale, and complexity are all increasing at the same time. Across the Rapid7 2026 Global Cybersecurity Summit, the focus was not just on how the threat landscape is evolving, but on how teams are adapting their approach to keep up.

The sessions brought together perspectives from across detection and response, exposure management, AI, and security operations, with a consistent emphasis on making better decisions earlier and with more confidence.

How modern attacks are starting across identity, cloud, and social engineering

Several sessions explored how initial access has shifted toward identity misuse, social engineering, and cloud misconfigurations. These entry points often blend into normal activity, making it harder for teams to distinguish between legitimate behavior and early-stage compromise.

Understanding how attacks begin has become a critical part of detection strategy. Rather than relying on a single signal, teams need to recognize how activity develops across multiple systems and how seemingly low-risk events can connect into something more serious.

What real incident response looks like inside modern MDR and SOC teams

The sessions focused on MDR and the SOC provided a closer look at how incidents unfold in practice. Investigations rarely follow a clean path, and analysts are constantly making decisions with incomplete information while attackers continue to move.

What stands out is how MDR extends the SOC beyond detection, combining continuous monitoring with human-led response to guide organizations through incidents as they happen. Alerts initiate the process, but outcomes depend on how teams interpret signals, prioritize actions, and manage tradeoffs under pressure across cloud, identity, and on-prem environments.

This view highlights the operational reality behind incident response, where coordination and judgment shape the outcome as much as the technology itself.

Why complexity is slowing security teams down

Security environments continue to expand, bringing more tools, more data, and more potential points of failure. Across the summit, speakers highlighted how fragmented visibility and unclear ownership can make it difficult to maintain a consistent view of risk.

The challenge is not eliminating complexity, but managing it in a way that allows teams to act effectively. Organizations that focus on clarity, ownership, and prioritization are better positioned to respond when signals start to converge.

How exposure management is reshaping risk prioritization

A recurring theme was the shift from vulnerability management toward exposure management. Vulnerability data provides insight into what exists, but it does not always reflect what creates meaningful risk.

Exposure management adds context by connecting vulnerabilities to assets, identities, and business impact. This allows teams to focus on what is reachable and relevant, helping them prioritize based on real-world risk rather than volume alone.

Frameworks like CTEM were highlighted as a practical way to structure this approach, creating a continuous process that connects discovery, validation, and response.

How AI is influencing both attacker behavior and defender workflows

AI is now influencing both sides of the security equation. Attackers are using it to scale reconnaissance and improve the effectiveness of social engineering, while defenders are applying it to reduce alert fatigue and accelerate analysis.

The discussion focused on how AI fits into real workflows, particularly in areas such as triage, enrichment, and investigation. Teams are finding the most value when AI is used to support decision-making rather than replace it, with transparency and oversight remaining central to adoption.

How security operations are shifting in practice

Across the summit, a clear direction emerged. Security operations are moving toward earlier action, more informed prioritization, and tighter integration between exposure, detection, and response.

This shift is reflected in how teams are building workflows that connect signals across environments and allow them to act before an incident escalates. It also reflects a broader move toward confidence in decision-making, where context and clarity are just as important as visibility.

Sound good? All sessions are available to catch up on, on demand here.

Final Countdown: Last Chance to Join the Rapid7 Global Cybersecurity Summit

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/it-last-chance-rapid7-global-cybersecurity-summit

The Rapid7 2026 Global Cybersecurity Summit is just around the corner, and with it, a final opportunity to join the conversations shaping how security teams are adapting to a rapidly changing landscape.

Over the past few weeks, we’ve shared a preview of what to expect, from the sessions and speakers to the themes running across the agenda. What has become increasingly clear is how closely these topics are connected. Security teams are being asked to move beyond reacting to incidents and instead understand how attacks begin, how they evolve, and how decisions can be made earlier with greater confidence.

What you will gain from attending

Across two days, the summit is structured to reflect how security teams actually operate. The first day builds a shared understanding of how the threat landscape has shifted, while the second day offers more focused sessions tailored to both leaders and practitioners.

Sessions such as The Reality of Running a SOC in 2026 and Inside the Modern SOC explore how attacks unfold in practice, following signals from initial access through to response. These discussions highlight how analysts interpret activity across identity, cloud, and endpoint environments, and how decisions are made when multiple signals compete for attention.

Other sessions, including Beyond the Vulnerability List and From Cloud Exposure to Runtime Attack, focus on how exposure is changing the way teams prioritize risk. The emphasis is on understanding context and how exposed assets actually are to attackers, helping teams determine which issues are most likely to lead to impact and where effort should be focused.

Alongside this, sessions like The AI Dilemma: Automating Defense Without Surrendering Judgment examine how AI is being applied within SOC workflows. The discussion moves beyond theory and looks at how teams are balancing automation with human oversight, ensuring that speed does not come at the expense of trust or accountability.

What’s changing for security teams right now

Security operations are evolving in response to changes in both attacker behavior and organizational complexity. Environments are more distributed, signals are more fragmented, and the time available to respond continues to shrink.

As a result, the focus is shifting toward earlier action, better prioritization, and more connected decision-making. This means linking exposure with detection, reducing unnecessary noise, and building workflows that allow teams to act with clarity when it matters most.

Across the summit, these ideas are explored from multiple perspectives, but they consistently point toward the same outcome. Teams that can connect context, visibility, and response are better positioned to reduce risk before it becomes an incident.

Secure your place

With the event approaching, this is the final opportunity to register and take part in these discussions. Whether you are responsible for strategy, operations, or day-to-day detection and response, the summit is designed to provide practical insights that can be applied immediately.

Join us on May 12–13 and see how security teams are putting these approaches into practice across real environments.

Register now

A Walkthrough of the 2026 Global Cybersecurity Summit Agenda

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/it-walkthrough-2026-global-cybersecurity-summit-agenda

The full agenda for the Rapid7 2026 Global Cybersecurity Summit is now live, and it gives a clearer sense of how the conversation around security operations is evolving.

Across two days, the sessions progress from a shared understanding of how threats are changing into a more detailed look at how teams detect, respond, and make decisions in practice.

Day 1: How threats evolve and how teams respond

The day opens with a keynote, Defense Starts Earlier Than You Think, where Brian Castagna is joined by Craig Robinson, Research Vice President at IDC, to examine why complexity has become the main barrier to effective security and what changes when teams start acting earlier.

That context carries into The Reality of Running a SOC in 2026, featuring Raj Samani alongside Rachel Tobac, CEO of SocialProof Security, and Graham Cluley, cybersecurity speaker and podcast host. The discussion focuses on how attacks actually begin, from identity misuse to cloud misconfigurations, and why defenders often fall behind as those attacks evolve.

In Customer Panel: How Clarity Beats Complexity, leaders including Debby Briggs, CISO at Netscout Systems, Raheem Daya, Chief Technology Officer at Target RWE, and Will Lambert from Culligan International share how they are simplifying their environments and focusing on outcomes rather than activity.

From there, Inside the Modern SOC: Who Carries You Through an Incident walks through a real investigation step by step, showing how alerts are triaged, decisions are made, and outcomes are shaped under pressure.

The conversation then turns to AI in The AI Dilemma: Automating Defense Without Surrendering Judgment, where the role of AI in the SOC is examined through the lens of trust, transparency, and how it supports analyst decision-making in practice.

In Beyond the Vulnerability List, the focus shifts to exposure management, looking at how organizations are moving beyond static vulnerability tracking and using exposure as an early signal to guide detection and response.

That idea of validation continues in Using Red Teaming to Power Preemptive MDR, where continuous adversary testing is used to prove detection coverage and refine response workflows before an incident occurs.

The day also includes a short look at Rapid7: What’s New and What’s Next, connecting recent innovations across exposure management, MDR, and AI to how teams operate in practice.

The closing session, Persistence Under Pressure, introduces a different perspective. Former Special Forces operator Jason Fox draws on real-world experience to explore preparation, understanding the adversary, and how teams make decisions when conditions are less predictable.

Day 2: Strategy for leaders, execution for practitioners

The second day builds on that foundation, with two dedicated tracks designed around how security teams actually work.

For security leaders, The CISO’s Role in Enterprise Transformation brings together perspectives from Craig Robinson and Horst Moll, CISO at Miltenyi Biotec, to explore how the role of the CISO is evolving beyond technical leadership into broader organizational influence.

That is followed by How Exposure Insights Reframe Risk and Security Decisions, which looks at how leaders define priorities and align teams when exposure data is tied more closely to real-world risk.

In A CISO’s Guide to MDR Accountability and Outcomes, the focus moves to how effectiveness is measured, shifting from activity-based metrics toward outcomes that reflect business impact.

The leader track closes with Customer Panel: What CISOs Would Do Differently If Starting Today, featuring CISOs including Jonathan Chow of Genesys and Tony Arnold of TSB Bank, reflecting on what they would change or simplify based on experience.

For practitioners, Hunt or Be Hunted: Frontline Tales of Detection walks through a real incident, showing how analysts decide what to investigate and how signals are correlated across environments.

The New Rules of Detection Engineering builds on that with insights from Steve Edwards, Director of Threat Intelligence Detection Engineering, focusing on detection-as-code and how teams prioritize signals in practice.

In From Cloud Exposure to Runtime Attack, Shauli Rozen, CEO and Co-founder of ARMO, and Ben Hirschberg, CTO and Co-founder, walk through a cloud attack scenario to show how risks escalate and how they can be interrupted earlier.

The practitioner track closes with IR in Practice: Tools, Tradecraft, and Adversary-Informed Investigation, where Shanna Battaglia and Michael Cohen demonstrate how open-source tools and real-world workflows come together during incident response.

Register and join the conversations

Taken together, the agenda reflects a shift that runs through every session. Security operations are moving toward earlier decisions, better prioritization, and a clearer understanding of what matters in the moment.

If you want to see how that shift is playing out across strategy, detection, and response, this is where those conversations come together.

Join us May 12–13 and explore the full agenda in practice.

Register now.

Five Things we Took Away from Gartner SRM Sydney 2026

Post Syndicated from Rapid7 original https://www.rapid7.com/blog/post/it-5-things-gartner-srm-sydney-2026

At this year’s Gartner Security and Risk Management Summit in Sydney, Rapid7 CISO Brian Castagna joined industry CISO Nigel Hedges for a fireside chat on the decisions security leaders are actually making right now. They discussed the real decisions being made right now about budgets, burnout, AI, and perspective on consolidation.

The conversation reinforced what we see across many organizations: SecOps is very much focused on protecting business resilience, enabling confident decisions by senior security leaders, and building programs that scale across people, platforms, and emerging technology. Let’s now take a look at some of the main highlights from this year’s Summit.

The business case for SecOps has shifted and boards are listening

The ‘invest in security or get breached’ pitch has run its course. Boards have heard it too many times; plus, it frames security as a cost center that only proves its value when something goes wrong.

We’re seeing it being replaced by a resilience narrative. In most incidents, the biggest business impact is operational disruption. Hours or days of downtime create immediate revenue loss, reputational damage, and perhaps worse still for some, regulatory exposure. CISOs who can connect their programs to that reality – translating incident data into business availability and financial risk – find it significantly easier to justify spend and shape investment decisions.

That shift in dynamic changes what gets measured and prioritized as well as how security leaders communicate upward to the board. Threat intelligence and kill chains still matter inside the SOC, but the ability to translate that to a clear risk narrative is fast becoming a leadership requirement in its own right.

Platform consolidation is growing, but it’s not binary

The platform-vs-best-of-breed debate was notably pragmatic. The real question is how to strike the right balance: Consolidate where it improves efficiency and visibility, retain point solutions where they materially reduce a specific risk.

On the ground, budget pressure has accelerated this. Fewer vendors, more integrated telemetry, and clearer operational ownership help make spend more defensible. The discussion framed consolidation through the lens of ‘control planes’ (endpoint, gateway, network), with shared telemetry as the connective layer.

A real-world example grounded the conversation: Build a global security program for a 5,000-person organization across 40 countries on a $3 million budget, using a selective mix of MDR, PAM, EPM, and targeted point solutions only where necessary. Throughout, the operating principle was simple in that every security investment needs to answer one question: What risk does this reduce, and importantly, what business outcome does it protect?

People remain the most difficult element of SecOps

Technology and process can be engineered, but people? They’re much harder. That was one of the most practical observations from the session, and it resonated with every security leader in the room.

The challenge goes beyond hiring technical talent to ensure organizations are building teams with the right mix of communication skills, cognitive diversity, motivation, and endurance. A common gap seen in the SOC is that many teams are strong technically but few can articulate risk effectively to executives. That matters because the value of SecOps increasingly depends on how well teams connect activity to impact.

At the same time, burnout remains a structural issue. When experienced analysts leave, institutional knowledge leaves with them. And no tool can replace that. For leaders, this reinforces the point that people strategy is core to the overall security strategy.

AI in SecOps is getting very real, and very practical

After a long hype cycle, the AI conversation is now far more grounded. The most credible use cases in SecOps are about helping teams manage volume, reduce noise, and move faster with better context.

The examples discussed in the session were telling: alert-assisted triage, natural-language log querying, incident summarisation, first-draft executive communications, and eventually more automated investigation workflows. The framing that landed best was AI as a ‘sidearm partner’; a force multiplier for experienced practitioners, rather than a substitute for judgment.

That distinction matters as human judgment is essential. But AI is becoming increasingly valuable for understaffed teams trying to scale operations and preserve the institutional knowledge that walks out the door when analysts move on.

Governing agentic AI begins with foundations you should already have

As the discussion turned to agentic AI, the focus centred on how more autonomous AI systems do introduce new governance questions, but many of the relevant controls already exist within mature security programs. Segmentation, least privilege, access management, and strong architectural boundaries remain the core defenses.

One analogy stuck: Just as graphite rods slow a nuclear chain reaction, controls like network segmentation and access boundaries can contain and constrain agentic behavior. The organizations best positioned for AI governance are often the ones that have already invested in zero trust principles and sound identity controls.

That reframes the conversation. AI governance isn’t a separate discipline,  it’s the extension of existing security foundations into how AI systems behave, access data, and operate within defined boundaries.

What this means for the road ahead

If there was a unifying message, it was that the modern SecOps mandate is bigger than prevention. The industry has, to some extent, over-rotated on stopping threats and under-invested in resilience. 

Security leaders require programs that communicate risk in business terms, make smart technology trade-offs, support their people, and adopt AI in ways that are practical and governable. The organizations that get this right will be the ones building strong foundations and using the right mix of platform, process, and intelligence to move faster and more confidently. 
Rapid7 is committed to being a partner to organizations looking to gain that confidence. Our exposure-informed MDR service empowers teams to adopt a more preemptive security posture by rapidly identifying high-impact exposures that could be imminent breach targets. Teams can also leverage expanded capabilities in data security posture management (DSPM) and compliance to help fortify assessment, prioritization, and response capabilities so they can further preempt attacks across the modern attack surface.

Top announcements of the What’s Next with AWS, 2026

Post Syndicated from AWS News Blog Team original https://aws.amazon.com/blogs/aws/top-announcements-of-the-whats-next-with-aws-2026/

Today at the What’s Next with AWS, Matt Garman, CEO of AWS, Colleen Aubrey, SVP Amazon Applied AI Solutions, Julia White, CMO of AWS, and OpenAI leaders discussed how they and their customers are changing how businesses operate with agents.

Here’s our roundup of the biggest announcements from the event:

Amazon Quick is an AI assistant for work that connects to all of them, learns what matters to you, and takes action on your behalf. Starting today, you can use the new desktop app, sign up for Free and Plus pricing plans, generate visual assets in the chat, and easily connect Quick to even more apps.

  • Quick’s new desktop app (Preview): You can create a personalized experience by staying connected to your local files, calendar, and communications without opening a browser.
  • New Free and Plus pricing plans for Quick: You can sign up within minutes using your personal email address or existing Google, Apple, Github, or Amazon credentials—no AWS account required.
  • Generate visual assets on the fly: Available today, Quick now lets you create polished documents, presentations, infographics, and images directly from the chat interface, no design skills or hours of formatting required.
  • Easily connect Quick to even more apps: Also available today, Quick is expanding its native integrations to include Google Workspace, Zoom, Airtable, Dropbox, and Microsoft Teams.

To learn more, visit the About Amazon News post.

Amazon Connect is expanding from a single product into a set of four agentic AI solutions designed to work within your existing workflows: Amazon Connect Decisions (supply chains), Talent (hiring), Customer (customer experience), and Health (health care).

  • Amazon Connect Decisions is a supply chain planning and intelligence solution that shifts teams from crisis management to proactive planning and decisioning. AI teammates, combining 30 years of Amazon operational science and 25+ specialized supply chain tools, adapt to your business, learn from your team, and continuously improve your operations.
  • Amazon Connect Talent (Preview) is an agentic AI hiring solution built for talent acquisition leaders managing scaled hiring. It delivers AI-led interviews, science-backed assessments, and consistent evaluation, helping recruiters hire high quality candidates faster while providing applicants with a flexible interview experience that reduces human preconceptions.
  • Amazon Connect Customer, previously known as Amazon Connect, delivers intelligent, personalized customer experiences across voice, chat, and digital channels. Amazon Connect Customer now offers new configuration capabilities that enable organizations to set up conversational AI in weeks, not months, and configure experiences without technical expertise.
  • Amazon Connect Health delivers agentic patient verification, appointment management, patient insights, ambient documentation, and medical coding — giving patients faster access to care, clinicians more time for care, and staff capacity for specialized work.

To learn more, visit the About Amazon News post.

AWS and OpenAI extended partnership
AWS and OpenAI are bringing the latest OpenAI models to Amazon Bedrock, launching Codex on Amazon Bedrock, and launching Amazon Bedrock Managed Agents, powered by OpenAI (all in limited preview), giving enterprises the frontier intelligence they want on the infrastructure they trust.

  • OpenAI models on Amazon Bedrock (Limited preview): The latest OpenAI models, including GPT-5.5 and GPT-5.4, will be available in preview on Amazon Bedrock. Use OpenAI’s frontier models through the same Bedrock APIs you already rely on, with unified security, governance, and cost controls. No additional infrastructure to configure, no new security model to learn.
  • Codex on Amazon Bedrock (Limited preview): You can access the OpenAI coding agent within the AWS environments where they already operate at scale. You can authenticate using their AWS credentials, process inference through Amazon Bedrock infrastructure, and apply Codex usage toward their AWS cloud commitments. Codex on Bedrock is available through the Bedrock API, starting with the Codex CLI, the Codex desktop app, and Visual Studio Code extension.
  • Amazon Bedrock Managed Agents, powered by OpenAI (Limited preview): Amazon Bedrock Managed Agents combines frontier AI models with trusted AWS infrastructure, enabling customers to quickly and easily build production-ready OpenAI-powered agents in the cloud. It is built with the OpenAI harness, which is engineered to unlock the full potential of OpenAI frontier models, delivering faster execution, sharper reasoning, and reliable steering of long-running tasks.

To learn more, visit the AWS What’s New post and About Amazon News post.

Get Motivated: What to Expect from Our Keynote at Rapid7’s Global Cybersecurity Summit

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/it-rapid7-global-cybersecurity-summit-keynote-rundown

Security teams prepare for incidents every day. Alerts are tuned, playbooks are built, and processes are tested. But when something actually happens, the challenge shifts. It becomes not just about making decisions under pressure, but how well that preparation has set teams up to make the right decisions when things heat up.

At this year’s Rapid7 Global Cybersecurity Summit, Persistence Under Pressure explores that shift directly. Former Special Forces operator Jason Fox draws on real-world experience where timing, clarity, and execution all have immediate consequences, and shows how that mindset applies to modern security operations.

In our keynote talk Persistence Under Pressure, former Special Forces operator Jason Fox brings experience from environments where timing, clarity, and execution all have immediate consequences. His session looks at how that mindset translates into modern security operations, where teams are expected to act quickly, often without complete information.

The parallels are clear: Incidents do not unfold in controlled conditions. Signals compete for attention, priorities shift, and decisions need to be made in real time. What matters in those moments is not just having the right tools, but knowing how to stay focused and act with confidence.

This session explores practical ideas that apply directly to security teams, from how preparation shapes response to how understanding the adversary influences decision-making, and why composure and clarity can make the difference when pressure builds.

It also reinforces a broader theme running throughout the summit. Preemptive security operations are not only about detecting threats earlier but about enabling better decisions across the entire lifecycle, from preparation through to response and recovery.

If you are looking to understand how security operations are evolving, this session offers a different but valuable perspective. One that connects strategy and technology back to the people responsible for making it work.

Join us May 12–13 and hear how these principles apply in practice. Register now.

3 Reasons to Attend our Global Cybersecurity Summit if you’re Focused on AI, Threats, and CTEM

Post Syndicated from Emma Burdett original https://www.rapid7.com/blog/post/it-why-attend-global-cybersecurity-summit-ai-exposure-management-ctem

Security teams are dealing with a different kind of pressure now. It is not just the volume of alerts or the pace of attacks, but also the gap between what teams can see and what they can act on with confidence.

That gap shows up in different ways. Threats move across identity and cloud in ways that are difficult to track, exposure data exists but often sits disconnected from response, and AI is being introduced into workflows without a clear role in decision-making.

This year’s Rapid7 Global Cybersecurity Summit brings those threads together as part of the same operational solution.

1. You need a clearer view of how attacks actually unfold

A lot of detection strategies still assume attacks follow a clean path. In practice, they do not. They start in one place, move quickly, and often rely on small gaps rather than obvious failures.

Sessions like The Reality of Running a SOC in 2026 break this down in detail, looking at how attacks begin with things like identity misuse or cloud misconfiguration, then evolve as defenders try to keep up. That matters because it changes how detection should be designed. Coverage alone is not enough if teams do not have the context created by strong exposure management to interpret what they are seeing.

That same idea carries into Inside the Modern SOC, where a real investigation is followed from first alert to outcome. It is a useful reminder that detection is only part of the problem.Deciding how to respond, and doing it quickly, is the critical next step.

2. Exposure only matters if it connects to action

Most teams already have some form of exposure management in place. The challenge is making it useful. A long list of vulnerabilities does not help much if it is not tied to how risk actually shows up in the environment.

Sessions like Beyond the Vulnerability List and From Cloud Exposure to Runtime Attack focus on that connection. They look at how exposures turn into active threats, often before any alert is triggered, and how teams can use that information to prioritize earlier.

Here’s the part people miss. Exposure is not just about knowing what is wrong. It is about understanding what matters now, based on how the environment is being used and how attackers are likely to move through it.

3. AI is only useful if it improves decisions

AI is already part of most security conversations, but the reality is nuanced. In some cases it helps reduce noise and speed up investigations. In others, it creates new questions around trust and transparency.

The AI Dilemma: Automating Defense Without Surrendering Judgment tackles this directly. It looks at where AI is helping in real SOC workflows, where it can get in the way, and why explainability matters if teams are going to rely on it. The discussion is grounded in how analysts actually work, not just what the technology promises.

There is also a broader point here. Attackers are using AI as well, which means the balance between speed and accuracy is becoming more important on both sides.

Join the conversation

Across these sessions, the common doesn’t stem from any single technology. It is how teams connect signals, context, and decisions in a way that holds up under pressure, which shows up in how threats are understood, how exposure is prioritized, and how AI is applied. It is also why the summit is structured the way it is, moving from shared context on day one into more focused, role-based sessions on day two.

More sessions and speakers will be added in the coming weeks, but the direction is already clear. Security operations are shifting toward earlier decisions, better prioritization, and fewer assumptions.

If your work touches AI, threat detection, or exposure management, this is where those conversations start to come together.

Join us May 12–13 and see how teams are approaching it in practice.

Register now.