On July 27, 2026, JetBrains published a security advisory for CVE-2026-63077, a critical unauthenticated vulnerability affecting all versions of TeamCity On-Premises. The issue is classified as deserialization of untrusted data and has a CVSS score of 9.8. An unauthenticated remote attacker with HTTP(S) access to a TeamCity server can exploit the agent polling protocol to bypass authentication checks and execute arbitrary operating system commands with the privileges of the TeamCity server process.
In the blog post that JetBrains shared in tandem with CVE publication, they stated that attackers who exploit the vulnerability can read stored credentials and compromise CI/CD pipeline integrity. The impact of successful exploitation depends on the operating system privileges granted to the TeamCity server process. At the time of disclosure, JetBrains stated that they were not aware of active exploitation.
Mitigation guidance
Organizations running TeamCity On-Premises should urgently prioritize updating to a fixed version, either via the TeamCity UI update workflow or by downloading and installing one of the following fixed versions:
TeamCity 2025.11.7
TeamCity 2026.1.3
All versions of TeamCity On-Premises are affected. Organizations that cannot upgrade can apply JetBrains’ security patch plugin to TeamCity 2017.1 and later. The plugin addresses only CVE-2026-63077; JetBrains recommends upgrading to a fixed version to receive other security updates. TeamCity Cloud customers do not need to take action.
In addition to patching, as a defense-in-depth measure, Rapid7 recommends restricting network access to TeamCity servers to only users and systems that must have it. For the latest mitigation guidance, please refer to the JetBrains security advisory.
Rapid7 customers
Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-63077 with a vulnerability check available in the July 28 content release.
On July 14, 2026, Microsoft published a security advisory addressing CVE-2026-58644, a critical remote code execution (RCE) vulnerability affecting on-premises Microsoft SharePoint Server deployments. The vulnerability, which carries a CVSS v3.1 score of 9.8 (Critical), results from the deserialization of untrusted data (CWE-502) and allows an unauthenticated attacker to execute arbitrary code.
Microsoft confirmed active exploitation of CVE-2026-58644, and the vulnerability was subsequently added to CISA’s Known Exploited Vulnerabilities (KEV) catalog on July 16, 2026. In parallel, CISA published guidance recommending organizations immediately apply Microsoft’s security updates and leverage Microsoft Defender and AMSI detections to identify exploitation attempts.
Affected products:
Microsoft SharePoint Enterprise Server 2016
Microsoft SharePoint Server 2019
Microsoft SharePoint Server Subscription Edition
Mitigation guidance
Organizations operating affected on-premises Microsoft SharePoint Server should prioritize remediation on an emergency basis.
Microsoft’s recommendations:
Apply the July 14, 2026 security updates for all affected SharePoint versions.
Verify that security updates completed successfully across all SharePoint servers.
Ensure Antimalware Scan Interface (AMSI) integration is enabled for every SharePoint web application.
Monitor Microsoft Defender and AMSI detections for indicators of attempted exploitation.
Initiate incident response procedures if exploitation artifacts are detected.
Microsoft and CISA recommend monitoring for the following security detections associated with observed SharePoint exploitation activity.
AMSI / Microsoft Defender detections:
Exploit:Script/SuspSignoutReqBody.A
Request body scanning
SharePoint Server Subscription Edition
Microsoft reports observed exploitation attempts are blocked by this signature.
Exploit:Script/ToolPaneAuthBypass.A
Request header scanning
Applies to SharePoint Server 2016, SharePoint Server 2019, and Subscription Edition.
Exploit:Script/ToolPaneAuthBypass
At the time of publication, no public IP addresses, domains, URLs, or additional network-based indicators of compromise have been widely disclosed.
Administrators should consult Microsoft’s advisory for the most current remediation guidance and update availability.
Rapid7 customers
Exposure Command, InsightVM, and Nexpose
Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-58644 with an authenticated vulnerability check available since the July 14 content release.
On July 14, 2026, SonicWall published a security advisory addressing two vulnerabilities affecting SMA1000 Series remote access appliances, including the critical server-side request forgery (SSRF) vulnerability CVE-2026-15409 (CVSS 10.0) and the high-severity code injection vulnerability CVE-2026-15410. The advisory urges customers to immediately apply the latest platform hotfix releases.
Successful exploitation of CVE-2026-15409 permits an unauthenticated attacker to open a websocket-based tunnel to arbitrary localhost-only services, while CVE-2026-15410 is a local privilege escalation that permits an attacker with access to an internal service listening on port 8188 on localhost to execute arbitrary operating system commands as root via a malicious path traversal-based remove_hotfix workflow.
Both vulnerabilities are being actively exploited in the wild. Prior to SonicWall’s official vulnerability disclosure, Rapid7’s Managed Detection and Response team observed active, targeted zero-day exploitation of internet-facing SMA 1000-series appliances. In the SonicWall advisory, exploitation in the wild was noted, and both CVE-2026-15409 and CVE-2026-15410 have been added to CISA’s Known Exploited Vulnerabilities (KEV) catalog. Given the confirmed exploitation activity and the critical unauthenticated impact of the vulnerabilities, organizations should prioritize remediation of SMA1000 appliances on an emergency basis. A Python proof-of-concept for CVE-2026-15409 is available here for exposure validation, and a Metasploit module for the chain is in development.
Affected products include SonicWall SMA1000 Series models 6210, 7210, and 8200v running:
12.4.3-03245
12.4.3-03387
12.4.3-03434 (platform-hotfix)
12.5.0-02283
12.5.0-02624
12.5.0-02800 (platform-hotfix)
These vulnerabilities do not affect SSL VPN functionality on SonicWall firewalls or the SMA 100 Series product line.
Technical overview
The primary vulnerability is in a websocket proxy feature, accessed via the path /wsproxy on the affected “SonicWall WorkPlace” application (served on port 443 by default). This feature permits a netcat-like TCP tunnel to arbitrary hosts and ports, which are provided by the user in URL parameters. By providing host values that point to localhost, the attacker can access local SonicWall appliance system services behind the firewall to send and receive arbitrary TCP traffic to and from them. This is the first-stage vulnerability, CVE-2026-15409, that Rapid7 MDR analysts are seeing attackers exploiting in the wild. With this capability, an attacker can reach and exploit less-hardened services running on the appliance, such as the Erlang application on localhost:1050 or the ctrl-service application on localhost:8188.
We developed an exploit targeting the Erlang process listening on localhost:1050 for remote code execution. Note that the provided cookie value is hardcoded for the Erlang process, based on our testing, so authentication is not required to establish code execution.
With code execution established, the attacker can escalate to root on the appliance by exploiting CVE-2026-15410, which is a path traversal in the remove_hotfix workflow of ctrl-service. This can be performed via the web console or by hitting port 8188 on the device. The attacker provides a hotfix value containing a path traversal sequence to a malicious script, such as “../../../../var/tmp/privesc”. The system executes the script as root and (typically) reboots the appliance immediately after. An example malicious request achieving privilege escalation by leveraging this from the web panel is depicted below:
If the provided hotfix file does not exist, a reboot does not occur. If the provided file exists, the system reboots after it chmods and executes the file. Below is a system monitor (pspy) depicting output of this occurring during exploitation:
A Python proof-of-concept for CVE-2026-15409 is available here; a Metasploit module for the chain is in development.
Mitigation guidance
Organizations operating SonicWall SMA1000 appliances should immediately upgrade to the latest platform hotfix releases.
Fixed versions are:
Product
Fixed Version
SMA1000 Series (6210, 7210, 8200v)
12.4.3-03453 (platform-hotfix) or later
SMA1000 Series (6210, 7210, 8200v)
12.5.0-02835 (platform-hotfix) or later
There are no workarounds available.
Because active exploitation has been confirmed, organizations should not rely solely on patching. SonicWall additionally recommends:
Performing a thorough forensic review for indicators of compromise.
Re-imaging physical appliances or redeploying virtual appliances if compromise is identified.
Changing user and administrator passwords.
Resetting TOTP tokens following confirmed compromise.
Customers should consult the SonicWall security advisory for the latest remediation guidance and platform hotfix availability.
Observed exploitation
Prior to SonicWall’s official vulnerability disclosure, our Managed Detection and Response team observed active, targeted exploitation of internet-facing SMA 1000-series appliances. Threat actors were primarily leveraging the perimeter appliance as a stealthy initial access vector, executing commands on the operating system by bypassing traditional input validation controls. Once they established a foothold on the appliance, the actors systematically extracted high-value credentials, active session databases, and Time-Based One-Time Password (TOTP) multi-factor authentication (MFA) seed configurations. This local harvesting was designed to ensure long-term, persistent access that could survive standard network-level remediations.
With these harvested resources, the threat actors quickly shifted to lateral movement, pivoting from the compromised appliance directly into the internal corporate network. Specifically, we observed a sequence of anomalous, VPN-less Active Directory authentications targeting core domain controllers. These authentications originated directly from the appliance’s internal IP address, using atypical, non-corporate workstation client names (such as kali or other non-inventory hostnames) under the context of the appliance’s integrated LDAP service account. This unique behavior of direct, machine-level lateral movement with no corresponding active VPN tunnel confirmed that the appliance itself had been fully compromised and was acting as an unmonitored backdoor into the corporate directory infrastructure.
Artifacts or evidence sources and IOCs
Rapid7 recommends reviewing appliance logs for evidence of active exploitation, including the following characteristic behaviors and specific log indicators:
Characteristic Behaviors
Websocket exploit IOC log patterns: extraweb_access.log entries containing the strings (“GET” AND “wsproxy” AND “=-3389” AND “ 101 “) indicate interactions with the niche affected service. If suspicious host parameter values such as “0.0.0.0”, “localhost”, or “::ffff:127.0.0.1” are present, that’s indicative of likely exploitation of CVE-2026-15409. Note that “serviceType=SSH” was used in our published materials, but options such as “serviceType=TELNET” are viable alternatives.
Hotfix removal exploit IOC log patterns: The ctrl-service.log shows the hotfix-removal utility (/usr/local/bin/remove_hotfix) being invoked with traversal sequences pointing to attacker-staged shell script payloads (e.g., ../../../../../../tmp/sma1000_5c47.sh). This is indicative of successful exploitation of CVE-2026-15410.
Internet-facing probing: Enumeration of the SMA portal, including repeated requests to /auth1.html, path-traversal attempts, and generic file/enumeration requests (e.g., /.env, /api/sonicos/is-sslvpn-enabled).
Authentication activity: Authentication-API activity against /__api__/logon/<session-id>/authenticate.
Sensitive path access: Access to sensitive appliance paths such as /tmp/temp.db*, consistent with theft of stored session data.
AD/Service Account Compromise: NTLM logons (Windows Event ID 4624, logon type 3) into internal domain controllers sourced from the appliance’s internal IP address, using attacker-controlled workstation names (e.g., kali) without a corresponding VPN session.
extraweb_access.log: Requests to /__api__/login or /__api__/logout returning HTTP 200, and requests to /wsproxy containing suspicious host parameters returning HTTP 101.
Configuration artifacts
/var/lib/unit/conf.json containing routes for /__api__/login or /__api__/logout, which are not present in legitimate configurations.
Atomic Indicators
F.N.S Holdings Limited (ASN – 206092): The threat actor(s) utilized varying IP addresses, but they belonged to the VPN hosting provider FNS Holdings Limited. Limit or block access to FNS Holdings Limited if there is no business need. For reference, the IP addresses we observed were:
45.131.194.0/24
45.146.54.0/24
63.135.161.0/24
173.239.211.0/24
193.37.32[.]179
193.37.32[.]214
216.73.163[.]151
216.73.163[.]158
If any indicators of compromise are identified, organizations should treat the appliance as compromised and follow SonicWall’s recovery guidance.
Rapid7 customers
Organizations should prioritize identifying all internet-facing SonicWall SMA1000 appliances and determine whether affected software versions remain deployed. Given SonicWall’s and Rapid7’s confirmation of active exploitation, exposed appliances should be considered high-priority assets for remediation.
Security teams should also review available authentication, web access, and appliance management logs for the indicators published by SonicWall to determine whether follow-up incident response activities are warranted.
Exposure Command, InsightVM, and Nexpose
Exposure Command, InsightVM, and Nexpose customers will be able to assess exposure to CVE-2026-15409 and CVE-2026-15410 with authenticated vulnerability checks available in the July 15 content release.
Rapid7 has been named a Major Player in the IDC MarketScape: Worldwide SIEM 2026 Vendor Assessment (#US54126826, June 2026).
This is the first IDC SIEM MarketScape to bring the enterprise and SMB markets into a single evaluation, and we believe it arrives at a time when the way teams buy and run a SOC is changing quickly. Security teams are no longer evaluating detection and response in isolation. They want their threat data, automation, and view of the attack surface working together, rather than spread across a stack of disconnected tools.
We believe Incident Command reflects that shift by bringing threat data, automation, and attack surface context into one platform instead of leaving teams to work across disconnected tools. It also speaks to a broader change in security operations, where context matters more, speed matters more, and teams need a clearer path from alert to action. That same direction runs through Rapid7’s wider point of view on preemptive security: exposure, detection, and response work better when they inform each other through shared context, AI, and human expertise.
Incident Command brings detection, response, and exposure context together
Incident Command brings SIEM, SOAR, attack surface management, and threat intelligence together on a shared data model. That gives analysts access to asset risk, vulnerability data, and exposure context during an investigation, so they can understand whether a detection affects a high-risk, internet-facing asset without having to jump between separate products.
According to the IDC MarketScape, “Incident Command is a strong fit for midmarket to enterprise organizations that want a fully integrated security operations platform with predictable costs.”
The teams we talk to are tired of stitching tools together and dealing with surprise ingestion bills. They want fewer blind spots, faster investigations, and a clearer answer to what is urgent and what to do next. Incident Command addresses that by bringing exposure context, threat intelligence, and response automation into the SIEM workflow, helping teams investigate faster and act with more clarity. For organizations looking for additional managed coverage, Rapid7 MDR is available as a separate offering. As attacks move faster and environments become harder to manage, security operations work better when exposure, threat, and response data are connected through an open platform that gives teams the context they need to move with more speed and clarity.
AI and automation, pressure-tested by a global SOC
Many vendors talk about AI in the SOC. For customers, the more important question is how those capabilities are developed, tested, and refined so they are useful in real investigations rather than just sounding good in a product story. We believe the IDC MarketScape called out what that means in Rapid7’s case:
“AI models and automation capabilities are tested in the MDR SOC before release to product customers, providing a feedback loop between managed service outcomes and product development that organizations without their own MDR equivalent cannot replicate.”
Our MDR analysts work real incidents across thousands of customer environments every day. The detections, triage models, and automation that come out of that work are tested against live attacks before they reach product customers. That feedback loop helps make the AI Engine more useful in practice by handling repetitive work such as classifying alerts, compiling evidence, and surfacing next steps, while analysts spend their time on the decisions that actually require human judgment. That balance also reflects Rapid7’s broader platform story: AI-powered, backed by human expertise.
What we believe this IDC MarketScape recognition says about the future of SIEM
The 2026 IDC MarketScape is a useful signal of where the market is heading. Organizations are looking for platforms where exposure and detection inform each other instead of living in separate systems, and where AI helps teams move faster without removing the human judgment needed to make the right call. We believe that is very much in line with the platform Rapid7 has been building through Incident Command and the wider Command Platform story. We’ll continue investing in the AI Engine, deeper attack surface context, and the integrations customers rely on. The goal remains straightforward: help defenders move faster to keep their environment safe, investigate with more context, and respond with machine speed and confidence.
Want to see Incident Command in action? Request a demo or explore the packages built to meet your team where it is.
Security leaders rarely struggle to gather data, but they often struggle to turn that data into something clear and meaningful for the business. In a typical week, a CISO might receive a report listing hundreds or even thousands of vulnerabilities, most of them accompanied by CVSS scores that make the entire list look urgent, while also managing the wider set of operational, regulatory, and strategic demands that already come with the role.
That difficulty becomes more obvious when the same information has to be carried into the boardroom, where the questions are rarely about CVE IDs or exploit counts in isolation. What leadership wants to understand is whether the organization’s revenue, uptime, legal exposure, or broader resilience could be affected, and how quickly those risks need to be addressed.
This is where many security programs lose momentum, because the technical view of severity does not always line up neatly with the business view of consequence. Bridging that gap has traditionally been slow, manual work, which is one reason AI is starting to matter more in vulnerability management: it can help translate technical findings into business context that is clearer, faster to act on, and easier for leadership to understand.
Why CVSS alone does not reflect real-world business risk
For years, the industry has relied on CVSS as a quick way to judge urgency, and while the framework does account for factors such as attack vector, attack complexity, and other attack requirements, the score is still calculated in isolation and often misses the conditions that shape real risk inside an organization. A CVSS 9.8 vulnerability affecting a legacy printer in a segmented branch office may look critical on paper, but it is unlikely to carry the same business impact as a 7.5 vulnerability affecting an internet-facing database that holds sensitive customer data.
One of the long-standing weaknesses of static scoring is that it tells you how severe a flaw may be in theory, but not how much disruption it could cause in your own environment, how exposed the affected asset is, or how closely it is tied to a revenue-generating or business-critical process. That is where AI becomes more useful, because it can add the missing context that helps security teams judge not just how serious a vulnerability looks, but how much it matters in practice.
Machine learning models can now process a much broader set of inputs, including attacker activity, exploit availability, internal network topology, and the business value attached to the asset or process involved. Rather than leaving teams with a static queue of scores, that creates a live view of risk shaped by reachability, exposure, and business consequence, making it easier to separate technical severity from actual organizational risk.
How AI helps connect vulnerabilities to business impact
One of the more practical ways AI can improve vulnerability management is by helping security teams connect technical findings to the parts of the business they actually affect. A vulnerability tied to an obscure IP address may not mean much on its own, but the picture changes quickly when that asset is identified as part of a regional payment system, a customer-facing portal, or a supply chain application the business depends on. That kind of asset attribution has traditionally taken time, context, and manual investigation. AI can help shorten that process by linking technical findings to business function much more quickly.
Instead of relying only on severity scores or yesterday’s alerts, AI can weigh a broader set of signals, including exploit activity, attacker behavior, asset exposure, and internal topology, which gives security teams a more grounded way to judge where risk is most likely to become operationally significant. The benefit is not simply speed, but a clearer picture of which vulnerabilities are most likely to affect revenue, uptime, or business continuity if they are left unresolved.
At the leadership level, this same approach can help turn a large volume of technical output into something more usable. Rather than forcing CISOs to manually translate thousands of low-level alerts into board-facing language, AI can support that reporting by summarizing likely business impact, highlighting where exposure is growing, and making it easier to explain how remediation work is reducing financial and operational risk.
Two vulnerabilities, two very different business outcomes
To see how this plays out in practice, it helps to compare two vulnerabilities that might appear similarly urgent in a standard scanner, but look very different once business context is added.
Vulnerability A: The ghost in the machine
A scanner flags a CVSS 9.8 critical remote code execution flaw in an aging media server. On paper, that score suggests immediate attention. Once more context is added, the picture changes. The asset sits on a segmented guest Wi-Fi VLAN, has no path to the corporate core, and has not been linked to in-the-wild exploitation for more than two years. In practical terms, the business impact is low. The issue still needs to be addressed, but it is unlikely to justify urgent remediation ahead of higher-consequence exposures.
Vulnerability B: The quiet threat
A second finding carries a lower CVSS 7.2 high severity score, but affects a common web framework running on the organization’s primary customer portal. When AI correlates that vulnerability with asset and business context, the risk profile changes quickly. The portal is identified as a critical business process, estimated to support $250,000 in transactions per hour, while external signals point to growing exploit interest around the same framework. In that case, the business impact is far more serious. What looks like a lower-priority technical issue becomes a potential source of revenue disruption measured in millions per day.
This is where AI-assisted prioritization becomes useful. It helps teams move beyond the assumption that the highest score always deserves the fastest response and instead focus on the vulnerabilities most likely to create operational or financial harm. In practice, that means spending less time working through a queue in score order and more time reducing the exposures that matter most to the business.
How AI helps CISOs explain vulnerability risk in business terms
When security leaders can move beyond reporting how many patches were deployed and begin showing how exposure is changing in financial or operational terms, the conversation becomes much more useful. A reduction in mean time to remediate may matter to a security team, but it carries more weight at the leadership level when it is tied to a lower likelihood of downtime, reduced regulatory exposure, or less risk to a revenue-generating service.
When vulnerability data is tied to business context, it becomes easier to justify automation, tooling, or headcount based on their contribution to resilience, continuity, and measurable risk reduction, rather than on activity alone. At that level, the conversation is less about severity scores and more about what is exposed, what it could affect, and where action matters most.
One of the more practical benefits of AI is that it can help security teams explain risk in a way leadership can act on. Instead of adding another layer of technical output, it can support clearer reporting on why one issue matters more than another, what is most likely to affect the business, and where action should come first.
As attack surfaces expand and exploit timelines continue to shrink, the gap between technical findings and business understanding will only become harder to manage. Organizations that can connect those two views more effectively will be in a much stronger position to prioritize the right work, explain risk more clearly, and make vulnerability management a more meaningful part of business decision-making.
On June 9, 2026, Ivanti published a security advisory for two critical vulnerabilities affecting Ivanti Sentry (formerly known as MobileIron Sentry), which per the vendor website is an “in-line gateway that manages, encrypts, and secures traffic between the mobile device and back-end enterprise systems”. The most severe issue, CVE-2026-10520, is an OS command injection vulnerability with a CVSS score of 10.0 that allows a remote unauthenticated attacker to achieve remote code execution (RCE) with root privileges. The second vulnerability, CVE-2026-10523, is an authentication bypass vulnerability with a CVSS score of 9.9 that allows a remote unauthenticated attacker to create arbitrary administrative accounts and obtain full administrative access. Ivanti has stated that they are not aware of any customers being exploited by either of these vulnerabilities at the time of disclosure.
Authentication Bypass Using an Alternate Path or Channel (CWE-288)
On June 10, 2026, watchTowr published a technical analysis of CVE-2026-10520 that includes a proof-of-concept (PoC) exploit for unauthenticated RCE. Given the trivial nature of exploitation and the availability of a public PoC, exploitation in-the-wild is likely to begin. Ivanti Sentry has featured on the CISA KEV list twice in the past (for the vulnerabilities CVE-2023-38035 and CVE-2020-15505), so we know threat actors will likely target this product.
Organizations running affected versions of Ivanti Sentry should remediate these issues on an urgent basis before exploitation in-the-wild begins.
Technical overview for CVE-2026-10520
Based upon the technical analysis by watchTowr, CVE-2026-10520 resides in the ConfigServiceController class within the Sentry web application, which is accessible via a POST request to the unauthenticated endpoint /mics/api/v2/sentry/mics-config/handleMessage.
The handleMessage endpoint accepts an attacker supplied message parameter that is parsed as an internal configuration command. This ultimately results in arbitrary OS command execution as root with an attacker control OS command. Shown below is an example HTTP request generated by the public PoC to execute the id command on an affected system:
A vendor-supplied update is available to remediate both CVE-2026-10520 and CVE-2026-10523. The following versions of Ivanti Sentry are affected:
Ivanti Sentry 10.7.0 and below
Ivanti Sentry 10.6.1 and below
Ivanti Sentry 10.5.1 and below
The following fixed versions of Ivanti Sentry remediate both vulnerabilities:
Ivanti Sentry 10.7.1
Ivanti Sentry 10.6.2
Ivanti Sentry 10.5.2
Given the critical severity of these vulnerabilities, the availability of a public PoC exploit for CVE-2026-10520, and the unauthenticated attack vector, Rapid7 strongly recommends updating affected Ivanti Sentry appliances on an urgent basis, outside of normal patching cycles.
Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-10520 and CVE-2026-10523 with unauthenticated vulnerability checks expected to be available in the June 11 content release.
On June 8, 2026, Check Point published a security advisory for CVE-2026-50751, a critical authentication bypass vulnerability affecting Check Point Remote Access VPN, Mobile Access, and Spark Firewall products. The vulnerability affects deployments configured to use the deprecated IKEv1 key exchange protocol where gateways accept legacy Remote Access clients and do not require a machine certificate for connections.
CVE-2026-50751, classified as improper authentication (CWE-287), has a CVSS score of 9.3. The vulnerability stems from a logic flow weakness in how Remote Access and Mobile Access components validate certificates during IKEv1 key exchange; successful exploitation allows an unauthenticated attacker to establish a VPN session without providing valid credentials. Per the vendor, additional post-authentication activity is required to access internal resources or escalate privileges.
Check Point has indicated that CVE-2026-50751 is being actively exploited in the wild, with observed activity dating back to May 7, 2026 and an increase in early June. The vendor characterizes the campaign as limited in scope, affecting several dozen organizations. At least one incident has been linked to a Qilin ransomware affiliate, which Check Point assesses with medium confidence.
Separately, during its investigation Check Point identified a related vulnerability, CVE-2026-50752 (CVSS 7.4), in the same IKEv1 code path that could enable a man-in-the-middle attack against site-to-site VPN tunnels under certain configurations. No exploitation of CVE-2026-50752 has been observed.
Check Point VPN products have been targeted by zero-day vulnerabilities in the past. In May 2024, CVE-2024-24919, a high-severity information disclosure vulnerability in Check Point Quantum Security Gateways, was exploited in the wild and subsequently added to the CISA Known Exploited Vulnerabilities (KEV) catalog. Organizations running affected Check Point products are urged to apply the available hot fixes and follow the vendor guidance to remediate these issues.
Mitigation guidance
Check Point has released hotfixes to remediate CVE-2026-50751. Affected organizations should apply the available updates on an emergency basis, without waiting for a regular patch cycle to occur.
The following products and versions are affected (Remote Access VPN, Mobile Access / SSL VPN, Spark Firewall):
R80.20.X (End of Support)
R80.40 (End of Support)
R81 (End of Support)
R81.10 (End of Support)
R81.10.X
R81.20
R82
R82.00.X
R82.10
Notably, four of the nine affected version branches (R80.20.X, R80.40, R81, R81.10) have reached End of Support. Organizations still running these versions should prioritize migration to a supported release.
For organizations unable to immediately apply the hotfix, Check Point has provided the following alternative mitigations:
Remove support for the legacy remote access client
Configure global properties for Remote Access VPN authentication to IKEv2 only
Set machine certificate authentication as mandatory
Enable IPS and download the latest signatures
Rapid7 strongly recommends looking for signs of compromise even after the hotfix has been applied. Per Check Point’s advisory, incident response teams should prioritize forensic log audits and configuration reviews starting from May 7, 2026, the earliest known date of exploitation.
For the latest mitigation guidance, please refer to the vendor advisory.
Rapid7 customers
Exposure Command, InsightVM, and Nexpose
Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-50751 with a vulnerability check expected to be available in the June 9 content release.
Indicators of compromise
Check Point has published the following indicators associated with the CVE-2026-50751 exploitation campaign. The attacker infrastructure consists of VPS hosts from several providers (Kaupo Cloud HK, Shock Hosting, Vultr Holdings), and Check Point notes that in some cases, the VPS region matched the geography of the targeted organization.
IP addresses:
45.77.149[.]152
209.182.225[.]136
38.60.157[.]139
162.33.177[.]101
45.76.26[.]42
144.208.127[.]155
38.54.88[.]201
38.54.107[.]167
66.42.99[.]200
File hashes (MD5):
52fda5c1b9704544f32ee98d9060e689
51d39aa39478beeac94f2d12f682ecce
Check Point observed post-exploitation attempts to retrieve ELF payloads from attacker-controlled servers, and identified ties to the Qilin ransomware operation based on binary analysis. For the full and most current list of IOCs, please refer to the vendor advisory.
On May 13, 2026, Palo Alto Networks published a security advisory for CVE-2026-0257, a medium severity authentication bypass affecting PAN-OS and Prisma Access when a specific configuration is present. Successful exploitation of this vulnerability allows a remote unauthenticated attacker to successfully establish a VPN connection through the GlobalProtect gateway of an affected appliance.
Rapid7 MDR identified successful exploitation across numerous customers, however we did not observe any indication of successful lateral movement from the devices. The earliest date for observed exploitation was May 17, 2026.
While the assigned CVSSv4 score indicates a medium severity, due to the circumstances surrounding this vulnerability Rapid7 urges that organizations treat this as a critical vulnerability. An authentication bypass in an edge facing enterprise VPN appliance can have significant impact to affected organizations. As such, organizations running affected appliances are urged to upgrade to a vendor supplied patch on an urgent basis.
Observed Attacker Behavior
On 2026-05-18 01:51:37 UTC, Rapid7 MDR responded to a ‘Suspicious VPN Authentication – Local Account Logon via Generic Non-Human Identity’ alert. During the initial investigation, Rapid7 observed a suspicious cookie authentication to the local admin account across multiple customer environments from the same hosting provider, Vultr.
Rapid7 MDR analyzed the Palo Alto tech support files across the impacted customers and observed that Cloud Authentication Service (CAS) was disabled and the GlobalProtect portal or gateway had authentication override cookies enabled. Based on these findings, MDR analysts concluded that this was likely exploitation of CVE-2026-0257. Subsequent analysis by Rapid7 Labs confirmed this was accurate by validating a successful proof-of-concept.
Rapid7 MDR observed a second wave of exploitation on May 21st. Due to the consistent MAC address, Rapid7 believes both waves of exploitation are likely from the same threat actor (TA). However, the second wave of compromises originated from the hosting provider, Dromatics Systems. In this wave of exploitation, Rapid7 observed VPN IP assignment following the cookie authentication, granting them access to the internal network. At this time, Rapid7 is unable to confirm why VPN assignment occurred only for a subset of exploited customers. Across multiple customers, Rapid7 observed successful exploitation to obtain the cookie, but did not observe the cookie being used to obtain a VPN session in 8 out of 10 impacted MDR customers. Rapid7 did not observe any follow-on activity in the two customer environments where a VPN session was established.
<14>May 21 01:54:39 FW-PA-A 1,2026/05/21 01:54:38,010101010101,GLOBALPROTECT,0,2818,2026/05/21 01:54:38,vsys1,gateway-auth,login,Cookie,,admin,US,DESKTOP-GP01,146.19.216.125,0.0.0.0,0.0.0.0,0.0.0.0,aa:bb:cc:dd:ee:ff,,6.0.0,Windows,"Microsoft Windows 10 Pro , 64-bit",1,,,"Auth latency: 1019ms, profile: SAML-o365-GP",success,,0,,0,GlobalProtect_External_Gateway,0101010101010101010 ,0x8000000000000000,2026-05-21T01:54:39.142-05:00,,,,,,30,241,35,0,,FW-PA-A,1,,",
GlobalProtect Authentication Log
Technical Analysis
Per the vendor advisory, we know the issue lies in a feature called “authentication override”. This feature allows a GlobalProtect portal or gateway to issue cookies to an authenticated user. The authenticated user can then use an authentication override cookie in future communications to the GlobalProtect portal or gateway in lieu of re-authenticating via credentials, akin to a bearer token. This is not a feature that is enabled by default.
We also know from reading the vendor advisory that the vulnerability requires a certain configuration in how certificates are used to encrypt and decrypt these authentication override cookies. Specifically, the certificate used to encrypt and decrypt authentication override cookies must not be the same certificate used for the GlobalProtect portal or gateway’s HTTPS service. This is a significant clue to how the vulnerability works.
To explore what an authentication override cookie looks like and how they are created, we can look at the implementation in the /usr/local/bin/gpsvc binary which implements the GlobalProtect service (Our testing appliance was running PAN-OS 10.2.8 in a vulnerable configuration). Inspecting the main_DoAuthLogin function, we see that if a HTTP form value of either portal-userauthcookie or portal-prelogonuserauthcookie is present during a POST request to /ssl-vpn/login.esp, authentication will be performed by a call to main_AuthWithCookie. This function will take the incoming encrypted cookie value stored in either portal-userauthcookie or portal-prelogonuserauthcookie, decrypt it and extract the cookies user name, domain name, host id, client OS, remote address, and timestamp (as auth override cookies have a lifetime after which they will expire).
If we look at the main_DecryptAppAuthCookie function we can begin to see the problem. The incoming encrypted cookie is base64 decoded and then decrypted using a private key. The decrypted content is then trusted implicitly, with no signature verification of any kind occurring after decryption.
The implication here is that anyone who knows the public key for the certificate used by the authentication override feature to encrypt and decrypt cookies, can successfully forge and encrypt an arbitrary authentication override cookie. The question then becomes, how does an attacker learn the correct public key to use in this attack?
This brings us back to the vendor’s advisory where they state “do not reuse the portal or gateway certificate, and do not share this certificate with other features or users”.
If a GlobalProtect portal or gateway has reused the certificate for encrypting and decrypting cookies with another feature, such as the HTTPS service of the portal or gateway, then a remote unauthenticated attacker can discover the public key for that certificate. In doing so the attacker will be able to successfully forge and encrypt arbitrary authentication override cookies. As these forged cookies will be successfully decrypted server side, they will be trusted and an authentication bypass will be achieved. An attacker can use a valid forged authentication override cookie to login and establish a VPN connection.
In addition to Exposure Command and InsightVM customers being able to assess their exposure with authenticated checks, a publicly available proof-of-concept script to test if an appliance is vulnerable to CVE-2026-0257 has been developed by Rapid7 Labs. The script will retrieve all certificates in the chain for the HTTPS service of either a GlobalProtect portal or gateway. Each certificate in the chain is iterated over and an authentication override cookie is forged using each certificate’s public key. This forged cookie is then tested against the GlobalProtect portal or gateway, and the script reports back if authentication was successful or not.
The usage of the script is shown below.
$ python3 forge_cookie.py --help
usage: forge_cookie.py [-h] --target TARGET [--port PORT] [--user USER] [--domain DOMAIN] [--host-id HOST_ID] [--client-os CLIENT_OS] [--client-ip CLIENT_IP] [--context {gateway,portal,both}] [--verbose]

Forge a GlobalProtect auth override cookie using the public key from TLS (CVE-2026-0257).

options:
  -h, --help            show this help message and exit
  --target TARGET       Target GP portal/gateway IP/hostname
  --port PORT           Target port (default: 443)
  --user USER           Username to forge cookie for (default: admin)
  --domain DOMAIN       Domain for cookie (default: empty)
  --host-id HOST_ID     Host ID for cookie (default: empty)
  --client-os CLIENT_OS
                        Client OS for cookie (default: Windows)
  --client-ip CLIENT_IP
                        Client IP in cookie (default: 0.0.0.0)
  --context {gateway,portal,both}
                        Context to test: gateway, portal, or both (default target)
  --verbose             Print full response
A successful invocation of the script against a vulnerable appliance is shown below. We can see the target’s GlobalProtect gateway accepted a forged authentication override cookie using the second certificate in the chain.
$ python3 forge_cookie.py --target 192.168.86.99 --user haxor
[*] Retrieving certificate chain from 192.168.86.99:443 ...
  Found 2 certificate(s) in chain:
  [0] CN=192.168.86.99 (RSA 2048 bits, CA=False)
  [1] CN=GP-Lab-CA (RSA 2048 bits, CA=True)

[*] Forging cookie for user 'haxor', testing each key

  Trying [0] CN=192.168.86.99
  [-] Failure - Gateway did not accepted the forged cookie
  [-] Failure - Portal did not accepted the forged cookie

  Trying [1] CN=GP-Lab-CA
  [+] Success - Gateway accepted the forged cookie
  Cookie: ng9ygxlaclylNXeSHcakXZPK06Fno0svVirz6RhRtA5mDmOaZyg/KMxUuM5lRvm1Rn1Z6vqaWQQPvQOHzwJnyldOmhUKy+HDMgIYtJ/kk3ypMqmFE7BbmPxnSKxKcQQbNIcxgkrhCwuJKwybuq0aaPVNzN9BSWmh1QmZj7oLjTEo9ExAXrm951mqYhh3+MgBCScaYqP23WzrC+vzqJB74sHoMUuFWIF8/sMYDMpvENOoI4nXAFCaRYSruW9FQQy5VTzNifNWkrYcdzDCXKiP8v4G098/2QoBbVoyHBZwbgHGBsRU3ZeSgoHjrhjxyotIshKVssUs8CRpuG2HlZBM0Q==
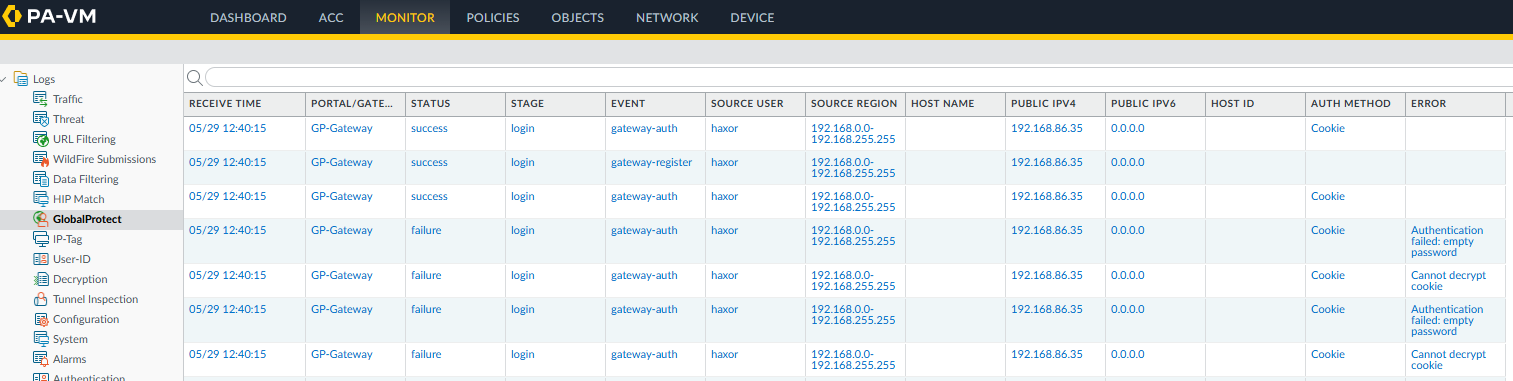
We can observe the successful authentication via the management interface, as shown below. The two initial failures correspond to the first certificate being used which was the incorrect certificate.
Figure 1: PAN-OS Management Interface
Mitigation Guidance
According to the Palo Alto Networks advisory, the following product versions are affected by CVE-2026-0257:
Product
Affected
Unaffected
PAN-OS 12.1
< 12.1.4-h6
< 12.1.7
>= 12.1.4-h6
>= 12.1.7
PAN-OS 11.2
< 11.2.4-h17
< 11.2.7-h14
< 11.2.10-h7
< 11.2.12
>= 11.2.4-h17
>= 11.2.7-h14
>= 11.2.10-h7
>= 11.2.12
PAN-OS 11.1
< 11.1.4-h33
< 11.1.6-h32
< 11.1.7-h6
< 11.1.10-h25
< 11.1.13-h5
< 11.1.15
>= 11.1.4-h33
>= 11.1.6-h32
>= 11.1.7-h6
>= 11.1.10-h25
>= 11.1.13-h5
>= 11.1.15
PAN-OS 10.2
< 10.2.7-h34
< 10.2.10-h36
< 10.2.13-h21
< 10.2.16-h7
< 10.2.18-h6
>= 10.2.7-h34
>= 10.2.10-h36
>= 10.2.13-h21
>= 10.2.16-h7
>= 10.2.18-h6
Prisma Access 11.2.0
< 11.2.7-h13
>= 11.2.7-h13
Prisma Access 10.2.0
< 10.2.10-h36
>= 10.2.10-h36
Affected products must have the authentication override feature enabled in either the GlobalProtect portal or gateway, and must reuse the authentication override cookie encryption and decryption certificate with another feature in order to be vulnerable. As a mitigation, affected products should either disable the authentication override feature or generate a new certificate to use exclusively for the authentication override feature.
Please refer to the vendor advisory for the latest guidance.
Rapid7 Customers
Managed Detection Response (MDR)
The following detection rules are available for InsightIDR and Managed Detection Response (MDR) customers:
Suspicious Authentication – Palo Alto GlobalProtect Cookie Authentication to Local Admin Account
Threat Intel (Rapid7 MDR SOC/IR) – VPN Authentication via Spoofed MAC Address
Threat Intel (Rapid7 MDR SOC/IR) – Indicator of Compromise Observed
Suspicious VPN Authentication – Local Account Logon via Generic Non-Human Identity
Suspicious VPN Authentication – Local Account
Suspicious Authentication – Vultr
Suspicious Authentication – Dromatics Systems
Exposure Command, InsightVM, and Nexpose
Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-0257 using an authenticated check available since the May 15 content release.
Known Indicators of Compromise
Low-cost hosting providers; frequent origin of sustained threat campaigns.
Item
Description
104.207.144.154
Threat actor source IP
146.19.216.119
Threat actor source IP
146.19.216.120
Threat actor source IP
146.19.216.125
Threat actor source IP
DESKTOP-GP01
Machinename observed in the GlobalProtect logs alongside Windows authentications first observed on May 21, 2026
GP-CLIENT
Machinename observed in the GlobalProtect logs alongside Linux authentications first observed on May 17, 2026
aa:bb:cc:dd:ee:ff
Spoofed MAC address observed in both waves of successful exploitation
On May 13, 2026, Palo Alto Networks published a security advisory for CVE-2026-0265, a signature verification vulnerability that facilitates authentication bypass on PAN-OS, the operating system that most Palo Alto Networks firewalls run. This vulnerability allows a remote unauthenticated attacker with network access to bypass authentication when Cloud Authentication Service (CAS) is enabled and attached to a login interface; the vulnerable configuration is non-default but common. CVE-2026-0265 affects PAN-OS on PA-Series and VM-Series firewalls, as well as Panorama (virtual and M-Series) appliances. Cloud NGFW and Prisma Access are not affected.
Palo Alto Networks assigned CVE-2026-0265 a “High” 7.2 CVSS score. The advisory states that the vulnerability’s severity scoring depends on interface exposure; according to the vendor, risk is highest for unrestricted management interfaces equipped with CAS, while other login portals, such as GlobalProtect gateways, are lower risk. However, the researcher who reported the vulnerability, Harsh Jaiswal of HacktronAI, publicly disputed the vendor’s severity rating. Jaiswal stated on social media that the vulnerability advisory misrepresents the criticality of the bug and the affected components; according to the HacktronAI research team, they successfully exploited CVE-2026-0265 to bypass authentication controls on multiple corporations’ GlobalProtect portals and establish VPN access. Jaiswal stated that internet-facing components are affected, and HacktronAI plans to disclose full technical details the week of May 18.
As of May 14, Palo Alto Networks has not confirmed exploitation in-the-wild of CVE-2026-0265, and there is no public proof-of-concept exploit available. However, given the researcher’s statements about the practical exploitability of this vulnerability and the pending disclosure of technical details, this will likely evolve. PAN-OS software has been a frequent target for threat actors; on May 6, 2026, the PAN-OS vulnerability CVE-2026-0300 was added to CISA’s Known Exploited Vulnerabilities (KEV) catalog. Patches for many affected version streams were published on May 13, and the remaining patches are expected on May 28, 2026.
Mitigation guidance
Organizations running PA-Series or VM-Series firewalls, or Panorama (virtual and M-Series) appliances, with Cloud Authentication Service (CAS) enabled should upgrade to a fixed version on an emergency basis. Patches are partially available, with many version stream fixes published on May 13 and additional version stream coverage expected on May 28. The following table outlines the affected and fixed versions:
PAN-OS version
Affected
Fixed
12.1
< 12.1.4-h5
< 12.1.7
>= 12.1.4-h5
>= 12.1.7 (ETA: 05/28)
11.2
< 11.2.4-h17
< 11.2.7-h13
< 11.2.10-h6
< 11.2.12
>= 11.2.4-h17 (ETA: 05/28)
>= 11.2.7-h13
>= 11.2.10-h6
>= 11.2.12 (ETA: 05/28)
11.1
< 11.1.4-h33
< 11.1.6-h32
< 11.1.7-h6
< 11.1.10-h25
< 11.1.13-h5
< 11.1.15
>= 11.1.4-h33
>= 11.1.6-h32
>= 11.1.7-h6 (ETA: 05/28)
>= 11.1.10-h25
>= 11.1.13-h5
>= 11.1.15 (ETA: 05/28)
10.2
< 10.2.7-h34
< 10.2.10-h36
< 10.2.13-h21
< 10.2.16-h7
< 10.2.18-h6
>= 10.2.7-h34 (ETA: 05/28)
>= 10.2.10-h36
>= 10.2.13-h21 (ETA: 05/28)
>= 10.2.16-h7 (ETA: 05/28)
>= 10.2.18-h6
Cloud NGFW
Not affected
N/A
Prisma Access
Not affected
N/A
Older unsupported PAN-OS versions should be upgraded to a supported fixed version.
To determine if an environment is vulnerable, the official advisory provides instructions to verify whether an authentication profile using CAS is enabled and attached to a login interface. Due to discrepancies in the information shared by the vendor and reporting researchers, Rapid7 advises patching instead of implementing workarounds, wherever possible.
For the latest official mitigation guidance, please refer to the vendor advisory.
Rapid7 customers
Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-0265 with authenticated checks expected to be available in the May 15th content release.
At Rapid7, our commitment to our partners is built on the foundation of the PACT (Partnering with Accountability, Consistency, and Transparency) program. Central to this mission is the Rapid7 Partner Academy, which was recently honored with a Gold Stevie Award in the 2026 American Business Awards® for Achievement in Collaboration and Partnership. This recognition underscores our dedication to providing world-class training that translates directly into partner success and customer resilience.
A new era of partner-led services
To meet the evolving needs of the cybersecurity landscape, Rapid7 Partner Academy has introduced specialized Partner Services Certifications. These role-based learning paths are designed to move beyond traditional “product training” by focusing on high-fidelity service delivery and outcome-driven results, including how to build, deliver, and scale services on Rapid7 solutions. The training and certification program was specifically recognized for its “Partner-First” design, which was built through extensive collaboration with our global partner ecosystem to ensure alignment with real-world sales and technical challenges.
Our award-winning partner services certification ecosystem focuses on three critical pillars of the Rapid7 Command Platform:
Partner Services for InsightIDR: Equips partners with the skills and knowledge necessary to effectively guide customers through the post-sale phases of the InsightIDR solution.
Partner Services for Exposure Command: Focuses on the transition from static vulnerability scanning to continuous attack surface validation, diving into the setup, management, and troubleshooting of Exposure Command.
Partner Services for Vulnerability Management: Empowers partners to provide impactful services around deployment, management, and ongoing support for InsightVM that drive customer success.
All three of these Partner Services Certifications enable our partners to deliver services around Rapid7 solutions from deployment and onboarding, to management and best practices for usage, to express health checks and troubleshooting. Upon successful completion of the course theoretical exam, you are eligible to enroll in the Services Validation Component. After validating your services capabilities, you will receive the prestigious distinction of achieving the Rapid7 Partner Services Certification and Badge. This achievement helps to differentiate your services to your customers and prospects with official recognition among the most capable Rapid7 MSSPs and service delivery partners.
Real-world impact: From training to execution
The Gold Stevie Award recognizes more than just curriculum—it recognizes the impact these certifications have on the partner’s ability to drive business and accelerate their profitability with Rapid7. By completing these Rapid7 Partner Academy certifications, partners gain:
Operational excellence: Technical specialists learn to deploy and manage Rapid7 solutions with a “Gold Standard” approach, ensuring high-fidelity results for customers.
Strategic alignment: Sales professionals are trained in the RSP (Rapid7 Sales Professional) methodology, allowing them to position Rapid7 as the preferred solution through effective discovery and objection handling.
Program economics: Certified partners can take full advantage of the 2026 PACT updates, which offer enhanced incentives and streamlined deal motions for partner-led growth.
Collaborating for success
The Stevie Award for Achievement in Collaboration and Partnership specifically applauds how Rapid7 integrated partner feedback into the curriculum development. This wasn’t just Rapid7 talking to partners; it was a co-innovation effort. By coordinating with partners and Rapid7 technical support stakeholders, we ensured that the Partner Academy content directly addresses the “last-mile” technical blockers partners face in the field.
The value and impact of Partner Academy is highlighted by the comments from the Stevie American Business Awards® judges:
“I’ve seen a lot of partner programs, and most are built for the vendor, not the partner. This one stands out…A 5X outperformance, 76% completion rate, 91% satisfaction, and an NPS of 68 all point to real value delivered, not vanity metrics. I’m especially impressed by the coordination behind it –100 contributors across 13 business units. That level of alignment is hard to achieve, and it shows strong leadership. The fact that the program was mentioned on an earnings call also signals clear strategic impact.”
“Overall, this is an outstanding and result-oriented program, and it sets the bar high for the partner enablement process. Exceeding the certification target by 5X within a significantly shortened timeframe speaks volumes for the relevance and execution of the program, and the creation of role-based, technically sophisticated learning paths speaks volumes for the focus on partner enablement.”
Celebrating our partners
This award is a shared victory with the thousands of partner individuals who have invested in their professional development through the Partner Academy. Whether you are a technical expert seeking to “Command the Attack Surface” or a sales professional looking to protect your margins, the Partner Academy is your gateway to success in the Rapid7 ecosystem.
Join the award-winning program and start your learning journey today!
As we continue to innovate, our goal remains the same: to provide the most transparent, consistent, and world-class enablement program in the industry. We invite all partners to officially become a Rapid7 PACT Partner to explore these award-winning certifications and start driving deeper impact for your customers today.
At this year’s Gartner Security and Risk Management Summit in Sydney, Rapid7 CISO Brian Castagna joined industry CISO Nigel Hedges for a fireside chat on the decisions security leaders are actually making right now. They discussed the real decisions being made right now about budgets, burnout, AI, and perspective on consolidation.
The conversation reinforced what we see across many organizations: SecOps is very much focused on protecting business resilience, enabling confident decisions by senior security leaders, and building programs that scale across people, platforms, and emerging technology. Let’s now take a look at some of the main highlights from this year’s Summit.
The business case for SecOps has shifted and boards are listening
The ‘invest in security or get breached’ pitch has run its course. Boards have heard it too many times; plus, it frames security as a cost center that only proves its value when something goes wrong.
We’re seeing it being replaced by a resilience narrative. In most incidents, the biggest business impact is operational disruption. Hours or days of downtime create immediate revenue loss, reputational damage, and perhaps worse still for some, regulatory exposure. CISOs who can connect their programs to that reality – translating incident data into business availability and financial risk – find it significantly easier to justify spend and shape investment decisions.
That shift in dynamic changes what gets measured and prioritized as well as how security leaders communicate upward to the board. Threat intelligence and kill chains still matter inside the SOC, but the ability to translate that to a clear risk narrative is fast becoming a leadership requirement in its own right.
Platform consolidation is growing, but it’s not binary
The platform-vs-best-of-breed debate was notably pragmatic. The real question is how to strike the right balance: Consolidate where it improves efficiency and visibility, retain point solutions where they materially reduce a specific risk.
On the ground, budget pressure has accelerated this. Fewer vendors, more integrated telemetry, and clearer operational ownership help make spend more defensible. The discussion framed consolidation through the lens of ‘control planes’ (endpoint, gateway, network), with shared telemetry as the connective layer.
A real-world example grounded the conversation: Build a global security program for a 5,000-person organization across 40 countries on a $3 million budget, using a selective mix of MDR, PAM, EPM, and targeted point solutions only where necessary. Throughout, the operating principle was simple in that every security investment needs to answer one question: What risk does this reduce, and importantly, what business outcome does it protect?
People remain the most difficult element of SecOps
Technology and process can be engineered, but people? They’re much harder. That was one of the most practical observations from the session, and it resonated with every security leader in the room.
The challenge goes beyond hiring technical talent to ensure organizations are building teams with the right mix of communication skills, cognitive diversity, motivation, and endurance. A common gap seen in the SOC is that many teams are strong technically but few can articulate risk effectively to executives. That matters because the value of SecOps increasingly depends on how well teams connect activity to impact.
At the same time, burnout remains a structural issue. When experienced analysts leave, institutional knowledge leaves with them. And no tool can replace that. For leaders, this reinforces the point that people strategy is core to the overall security strategy.
AI in SecOps is getting very real, and very practical
After a long hype cycle, the AI conversation is now far more grounded. The most credible use cases in SecOps are about helping teams manage volume, reduce noise, and move faster with better context.
The examples discussed in the session were telling: alert-assisted triage, natural-language log querying, incident summarisation, first-draft executive communications, and eventually more automated investigation workflows. The framing that landed best was AI as a ‘sidearm partner’; a force multiplier for experienced practitioners, rather than a substitute for judgment.
That distinction matters as human judgment is essential. But AI is becoming increasingly valuable for understaffed teams trying to scale operations and preserve the institutional knowledge that walks out the door when analysts move on.
Governing agentic AI begins with foundations you should already have
As the discussion turned to agentic AI, the focus centred on how more autonomous AI systems do introduce new governance questions, but many of the relevant controls already exist within mature security programs. Segmentation, least privilege, access management, and strong architectural boundaries remain the core defenses.
One analogy stuck: Just as graphite rods slow a nuclear chain reaction, controls like network segmentation and access boundaries can contain and constrain agentic behavior. The organizations best positioned for AI governance are often the ones that have already invested in zero trust principles and sound identity controls.
That reframes the conversation. AI governance isn’t a separate discipline, it’s the extension of existing security foundations into how AI systems behave, access data, and operate within defined boundaries.
What this means for the road ahead
If there was a unifying message, it was that the modern SecOps mandate is bigger than prevention. The industry has, to some extent, over-rotated on stopping threats and under-invested in resilience.
Security leaders require programs that communicate risk in business terms, make smart technology trade-offs, support their people, and adopt AI in ways that are practical and governable. The organizations that get this right will be the ones building strong foundations and using the right mix of platform, process, and intelligence to move faster and more confidently. Rapid7 is committed to being a partner to organizations looking to gain that confidence. Our exposure-informed MDR service empowers teams to adopt a more preemptive security posture by rapidly identifying high-impact exposures that could be imminent breach targets. Teams can also leverage expanded capabilities in data security posture management (DSPM) and compliance to help fortify assessment, prioritization, and response capabilities so they can further preempt attacks across the modern attack surface.
On April 28, 2026, cPanel issued a security update to fix a critical vulnerability affecting the cPanel & WHM and WP Squared products. In the cPanel release notes, the bug was described as “an issue with session loading and saving.” CVE-2026-41940, the identifier subsequently assigned on April 29, 2026, has a CVSS score of 9.8 and allows unauthenticated remote attackers to bypass authentication and gain unauthorized administrative access to the affected systems. First-party cPanel & WHM and WP Squared vendor advisories are available.
cPanel & WHM is web hosting control panel software used to manage websites and servers. WHM provides root-level administration, while cPanel acts as the user-facing interface. Successful exploitation of CVE-2026-41940 grants an attacker control over the cPanel host system, its configurations and databases, and websites it manages. A naive Shodan query for potential targets returns approximately 1.5 million cPanel instances exposed to the internet that may be vulnerable.
A managed cPanel host, KnownHost, stated that CVE-2026-41940 is actively being exploited in the wild, with speculation of targeted zero-day exploitation happening as early as February 23, 2026, prior to the vulnerability’s public disclosure. Security firm watchTowr has published a technical analysis and proof-of-concept exploit for CVE-2026-41940. As such, widespread exploitation in the wild is expected to be imminent.
Technical overview
Systems exposing the affected web service software are vulnerable by default.
As of April 29, 2026, a technical analysis and proof-of-concept exploit have been published by security firm watchTowr. CVE-2026-41940 is an authentication bypass caused by a Carriage Return Line Feed (CRLF) injection in the login and session loading processes of cPanel & WHM.
Before authentication occurs, `cpsrvd` (the cPanel service daemon) writes a new session file to the disk. The vulnerability allows an attacker to manipulate the `whostmgrsession` cookie by omitting an expected segment of the cookie value, avoiding the encryption process typically applied to an attacker-provided value. Attackers can inject raw `\r\n` characters via a malicious basic authorization header, and the system subsequently writes the session file without sanitizing the data. As a result, the attacker can insert arbitrary properties, such as `user=root`, into their session file. After triggering a reload of the session from the file, the attacker establishes administrator-level access for their token.
Mitigation guidance
Organizations running on-premise instances of cPanel & WHM or WP Squared should prioritize upgrading to a fixed version on an emergency basis. Some hosting providers have opted to temporarily institute workaround TCP port blocks for cPanel & WHM web services on ports 2083 and 2087. However, defenders are strongly advised to patch, rather than implement workarounds.
Affected Software:
cPanel & WHM 11.110.0 versions prior to fixed version 11.110.0.97
cPanel & WHM 11.118.0 versions prior to fixed version 11.118.0.63
cPanel & WHM 11.126.0 versions prior to fixed version 11.126.0.54
cPanel & WHM 11.132.0 versions prior to fixed version 11.132.0.29
cPanel & WHM 11.134.0 versions prior to fixed version 11.134.0.20
cPanel & WHM 11.136.0 versions prior to fixed version 11.136.0.5
WP Squared 11.136.1 versions prior to fixed version 11.136.1.7
Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-41940 with authenticated vulnerability checks expected to be available in the April 30, 2026 content release.
On March 30, 2026, a security advisory was published for a critical vulnerability affecting Nginx UI. Nginx UI is an open-source web interface to centralize the management of Nginx configurations and SSL certificates. The critical vulnerability, CVE-2026-33032, was reported in early March by Pluto Security researcher Yotam Perkal and subsequently patched on March 15, 2026. That same day, Pluto Security published a technical blog post with some vulnerability details.
CVE-2026-33032 is a missing authentication bug with a CVSS score of 9.8; as a result of missing authentication controls, an unauthenticated attacker can access a Model Context Protocol (MCP) server that can perform privileged operations on managed Nginx web servers. Systems are vulnerable in the default IP allowlist configuration, which allows any remote IP to access MCP functionality. Exploitation results in full attacker control of the managed Nginx service.
According to a Recorded Future report published on April 13, 2026, exploitation of CVE-2026-33032 in the wild has begun.
Mitigation guidance
Organizations running Nginx UI should prioritize updating on an urgent basis to remediate CVE-2026-33032. Additionally, to reduce exposure to future vulnerabilities affecting Nginx UI, defenders should ensure that network access to the Nginx UI management interface is strictly limited to those who must have it.
Affected versions:
According to the finder’s blog post, version 2.3.3 and prior are affected, and the fix is presentin version 2.3.4 and later. However the official CVE record states that versions 2.3.5 and below are affected. This discrepancy in affected version numbers makes it unclear as to the correct version required to remediate CVE-2026-33032. To avoid this version number discrepancy, users are advised to update to the very latest version (2.3.6).
Please read the vendor advisory for the latest guidance.
Rapid7 customers
Exposure Command, InsightVM, and Nexpose
Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-33032 with unauthenticated checks expected to be available in the April 17 content release.
On March 23, 2026, Citrix published a security advisory for a critical vulnerability affecting their NetScaler ADC (formerly Citrix ADC) and NetScaler Gateway (formerly Citrix Gateway) products. This vulnerability, CVE-2026-3055, which is classified as an out-of-bounds read and holds a CVSS score of 9.3, allows unauthenticated remote attackers to leak potentially sensitive information from the appliance’s memory.
The Citrix advisory states that systems configured as a SAML Identity Provider (SAML IDP) are vulnerable, whereas default configurations are unaffected. This SAML IDP configuration is likely a very common configuration for organizations utilizing single sign-on. Per the advisory, organizations can determine if they have an appliance configured as a SAML IDP Profile by inspecting their NetScaler Configuration for the specified string: add authentication samlIdPProfile .*
CVE-2026-3055 affects NetScaler ADC and NetScaler Gateway versions 14.1 before 14.1-66.59 and 13.1 before 13.1-62.23, as well as NetScaler ADC 13.1-FIPS and 13.1-NDcPP before 13.1-37.262. The advisory notes that only customer-managed instances are affected, not cloud instances managed by Citrix.
As of the advisory’s publication, there is no known in-the-wild exploitation and no public proof-of-concept (PoC) available. According to Citrix, the vulnerability was identified internally via security review. However, exploitation of CVE-2026-3055 is likely to occur once exploit code becomes public. Therefore, it is crucial that customers running affected Citrix systems remediate this vulnerability as soon as possible; Citrix software has previously seen memory leak vulnerabilities broadly exploited in the wild, including the infamous “CitrixBleed” vulnerability, CVE-2023-4966, in 2023.
Mitigation guidance
Organizations running affected on-premise instances of NetScaler ADC and NetScaler Gateway should prioritize upgrading to fixed versions on an emergency basis to remediate CVE-2026-3055.
Affected components:
NetScaler ADC and NetScaler Gateway versions 14.1, fixed in 14.1-66.59.
NetScaler ADC and NetScaler Gateway versions 13.1, fixed in 13.1-62.23.
NetScaler ADC 13.1-FIPS and 13.1-NDcPP, fixed in 13.1-37.262 (also referred to as 13.1.37.262 in the vendor advisory).
Please read the vendor advisory (CTX696300) for the latest guidance.
Rapid7 customers
Exposure Command, InsightVM, and Nexpose
Exposure Command, InsightVM, and Nexpose customers can assess exposure to CVE-2026-3055 on Citrix NetScaler ADC with an authenticated vulnerability check expected to be available in the March 24 content release.
There is a particular kind of energy that fills the room when partners gather with a shared mission. It is part strategy session, part reunion, part blueprint for what comes next. That spirit defined this year’s Rapid7 EMEA Partner Summit in Lisbon, Portugal. And that’s exactly what our partners around the world are set to experience at Rapid7’s Global Virtual Partner Kick-off on March 11th. During the Lisbon summit, it was exciting to see partners actively working with us to deliver better service to our joint customers. This level of interaction supports our core belief that partnerships shouldn’t be transactional, they should be a continuous collaboration resulting in a positive shared outcome.
Suzanne Swanson, Rapid7’s VP of Global Channel Partnerships, highlights this shared energy and commitment:
⠀
A shared path to customer success
A major focus of this year’s EMEA summit was what happens after the contract is signed.
“Today was really about how we work together once we’ve made the sale and brought the customer on board. How do we continue to add value and make them successful not only with Rapid7, but also in their general security posture?” noted Swanson.
Security is not a one-time event. It is an evolving discipline. Customers need consistent expertise, proactive detection and response, and partners who can wrap services, guidance, and strategic insight around technology investments.
At the Global Virtual Partner Kick-off on March 11th, we will share how our partners can:
Align with Rapid7’s 2026 strategy
Identify new pipeline and revenue opportunities
Gain competitive positioning insights
Understand regional priorities specific to local markets
Strengthen collaboration with Rapid7 leadership
Growth and retention move together, and partners are central to both.
PACT 2026: Building a program that works as hard as our partners
Partners attending the recent EMEA summit enjoyed an early view of the evolution of the Rapid7 PACT Partner Program for 2026, designed to make partnership easier, more rewarding, and more effective.
“This is more than just an annual program update, it’s a complete transformation, designed to fuel growth and unlock greater value for our partners,” said Kelly Hiscoe, Senior Director, Global Partner Programs & Experience. “On March 11, we’ll share a comprehensive look at the 2026 PACT Program during our Global Virtual Partner Kick-off.”
Partnerships built for scale
Organizations face a critical year ahead. Customers are merging platforms, and the demand for managed services is growing. Partners who align early, invest in training, and utilize the full Rapid7 portfolio will be in a prime position to lead.
This is a pivotal year for organizations everywhere. As customers streamline platforms and the demand for managed services accelerates, there is real opportunity ahead. We understand that by aligning early, investing in training, and making the most of the Rapid7 portfolio, our partners can truly position themselves as trusted security advisors.
Rapid7 partners: We can’t wait to see you on March 11th! Check your exclusive email invitation and register today for the Global Virtual Partner Kick-off.
Mark your calendars. The Rapid7 2026 Global Cybersecurity Summit returns May 12–13, bringing together security leaders, practitioners, and industry experts for two days of strategic leadership insight and hands-on operational guidance, designed to equip both decision-makers and defenders to build stronger, more resilient security programs.
This year’s theme is Preemptive Security Operations – a shift from reacting to threats to anticipating and neutralizing them before impact.
Security teams are navigating expanding attack surfaces, AI-accelerated threats, relentless alert fatigue, and increasing pressure to do more with less. The 2026 summit is designed to cut through that complexity and focus on what matters most, helping organizations move from reactive defense to confident, proactive operations.
What to expect from Rapid7’s 2026 summit
Whether you’re shaping security strategy at the executive level or defending systems inside the SOC, the summit will deliver actionable insights you can apply immediately.
Day 1 will focus on the big picture. Designed to bring together security leaders, decision-makers, and practitioners around a shared narrative, the first day will explore the paradigm shift shaping modern security operations. Sessions will examine how MDR is evolving beyond monitoring into proactive defense, how exposure management and threat intelligence are converging with it into unified risk strategies, and how AI is changing both attacker capabilities and defender workflows. The emphasis will be on clarity, alignment, and strategic direction, helping organizations rethink how their SOCs operate in an increasingly complex environment.
Day 2 will go deeper. Structured with dedicated tracks for security leaders and frontline practitioners, the second day will provide focused, role-specific content. Leaders will engage with sessions centered on governance, resilience, and executive accountability, while practitioners will dive into real-world detection scenarios, threat hunting methodologies, red teaming insights, and operational playbooks. This two-track approach reflects the reality facing modern security teams: strategy and execution must move forward together.
Why attend Rapid7’s global cybersecurity summit?
The Rapid7 Virtual Cybersecurity Summit is built for today’s reality where speed, clarity, and confidence matter more than ever. This year’s focus on Preemptive Security Operations reflects a shift from reacting to incidents toward anticipating and reducing risk before impact. Preemptive security means unifying visibility across the attack surface, aligning exposure with detection and response, and using AI and intelligence to prioritize what truly matters. It’s about giving security teams the insight and authority to act earlier, reduce uncertainty, and strengthen resilience across the organization.
If 2025 was about reacting faster, 2026 is about acting sooner, so save the date now and be part of the conversation shaping the future of preemptive security operations.
May 12–13, 2026 Rapid7 Virtual Cybersecurity Summit
Hospitals invest heavily in physical security: Clinical areas are access-controlled, sensitive rooms are locked, and patient records are governed by strict handling procedures. Network exposure does not always receive the same level of scrutiny.
Rapid7 Labs identified more than 30 UK-based systems responding to DICOM requests over Port 104, the default port used for medical imaging traffic. These systems were reachable from the public internet at the time of observation. Project Sonar was used to confirm service responsiveness only; no attempt was made to access patient records or exploit the systems.
When Port 104 is reachable from outside trusted networks without VPN restriction or encryption, the imaging service can be detected through routine internet scanning. This type of exposure matters because protocols like DICOM were developed for use within protected clinical environments where network access is already controlled.
Research into medical imaging infrastructure has found that when security best practices are not implemented, imaging systems and their acquisition gateways are placed on networks in ways that expose them to cybercriminal discovery. In one study of publicly accessible PACS (picture archiving and communication systems) servers, researchers reported that systems using default configurations or lacking appropriate network controls responded to internet scans and contained metadata such as patient identifiers, and the lack of basic protocol safeguards made them susceptible to data reconstruction and modification.
Why should DICOM not be internet-facing?
DICOM, or digital imaging and communications in medicine, is the international standard used to format, store, and transmit medical imaging data. It governs both the image itself and associated metadata, which can include patient identifiers, study details, acquisition parameters, and device information. Imaging modalities such as CT scanners and MRI machines use DICOM to send studies to Picture Archiving and Communication Systems (PACS), where images are stored and later retrieved by radiologists and clinicians.
DICOM operates at the application layer. Port 104 is the traditional default port associated with DICOM services, but the protocol is not limited to that port. PACS systems and imaging services may also communicate over web ports such as 80 or 443, and in some cases expose web-based or administrative interfaces over additional ports. In our broader research, we identified more than 15 PACS devices that were externally reachable, including systems accessible over standard web ports.
⠀
Figure 1: Clarify – PACS admin login portal.
⠀
In standard hospital deployments, DICOM services are intended to operate within segmented and trusted clinical networks. The protocol historically assumed that the surrounding network would provide access control and protection. When imaging systems or PACS services are reachable from public IP space, whether over Port 104 or web-based interfaces, they may respond to protocol negotiation or HTTP requests and disclose service-level information. In some configurations, metadata or system details can be retrieved without strong authentication controls.
That condition does not necessarily imply full access to imaging archives. It does mean that clinical infrastructure is externally discoverable and capable of interaction beyond its intended network boundary. The risk arises from that exposure, particularly when it is unintended or unmonitored.
Exposed DICOM servers in the UK: What Rapid7 Labs found
Using Project Sonar, Rapid7’s internet-wide exposure monitoring framework, we identified more than 30 UK-based healthcare systems responding to DICOM-related requests, including services associated with Port 104. The exposure was not limited to that port. Additional PACS and related healthcare systems were observed to be reachable over web ports such as 80 and 443, with more than 15 PACS devices directly accessible from public IP space.
⠀
Figure 2: UK-based exposed Healthcare systems to the Internet.
⠀
This methodology does not exploit systems or access patient records. It confirms whether a service is reachable and actively responding.
For healthcare organizations navigating increased regulatory scrutiny and rising cyber threats, this kind of medical device exposure is unnecessary risk.
The cybersecurity risks of exposed medical imaging systems
When a DICOM server is exposed to the internet, and the risk extends beyond technical misconfiguration, it introduces three primary threat categories:
Patient data exposure and healthcare identity theft
DICOM files typically contain structured metadata fields, which may include:
Patient name.
Date of birth.
Study identifiers.
Referring clinician information.
If a system allows metadata queries without authentication or encryption, those identifiers may be retrievable. Healthcare data retains long-term value because it cannot be reissued in the way payment credentials can.
Medical image manipulation and clinical integrity risks
Imaging workflows depend on trusted transmission between modalities, PACS servers, and diagnostic workstations. Research has shown that medical images can be altered using machine learning techniques under controlled conditions.
Exploitation requires access and technical capability, but exposure beyond intended network boundaries increases the potential attack surface. Clinical confidence depends on assurance that imaging data has not been modified in transit.
Ransomware entry points via PACS and imaging systems
Medical imaging systems like DICOM connect to PACS servers. If an exposed DICOM service provides a foothold, attackers may attempt lateral movement inside the network.
An exposed PACS server can quickly become operational ground zero – delaying procedures, disrupting diagnostics, and impacting patient care. As healthcare continues to face ransomware targeting across the UK and EU, edge systems and externally visible services are often initial access points.
UK healthcare attack surface exposure: DICOM is part of a wider pattern
The exposure of 30+ DICOM systems is concerning. But it is not isolated. A broader review of UK healthcare-associated IP space shows externally visible infrastructure including:
Cisco edge devices.
BigIP appliances.
Check Point firewalls.
Citrix NetScaler instances.
Ivanti Endpoint Manager Mobile.
SSL VPN portals.
Search for NHS registered names and filter on UK/GB:
Table 1: Externally visible technologies identified across UK healthcare-associated IP space.
⠀
These technologies are standard components of modern IT environments. The concern arises when exposure is unintended, unmonitored, or paired with delayed remediation. Public reporting in 2025 shows that ransomware groups continue to target healthcare following disclosure of vulnerabilities in edge appliances and remote access technologies. In several documented cases, exploitation occurred within days of vulnerability publication.
When more than 30 imaging systems are externally reachable, the underlying issue is unlikely to be a single isolated configuration error. It suggests incomplete visibility into which services are accessible from outside the organisation at any given moment.
⠀
Figure 3: Visibility of selected healthcare technologies over time.
External asset visibility and healthcare IT complexity
Healthcare IT environments evolve incrementally, with legacy protocols remaining operational because imaging equipment has long service lifecycles. This slow evolution can cause complications like:
Vendor default configurations are often inherited from initial deployment.
Cloud services introducing additional infrastructure layers that may not be consistently mapped alongside on-premise systems.
⠀
Figure 4: Ransomware groups observed targeting UK/EU healthcare in 2025.
⠀
Figure 5: Ransomware group activity observed around UK/EU healthcare in 2025.
Within this context, continuous external visibility becomes challenging. Many organisations do not maintain a real-time inventory of internet-facing services across all owned IP ranges. And so, without deliberate intent, a DICOM server or medical device can become externally reachable., Until specifically identified, the exposure can persist. The lesson?Infrastructure designed for ease of deployment can accumulate risk when oversight is periodic rather than continuous.
How to reduce DICOM and medical device exposure
As ransomware groups accelerate and exploitation windows shrink, it would be easy to frame exposure as oversight. But that diagnosis would miss the point.
The issue is not a lack of cybersecurity awareness within the NHS. It is the structural complexity of modern healthcare IT environments, with legacy protocols continuing to operate alongside newer systems.
Vendor-default configurations are often inherited rather than re-architected.
Third-party integrations expand the digital perimeter beyond the hospital campus.
Remote access services enable flexible care delivery, while cloud adoption accelerates faster than traditional governance models can adapt.
In this kind of environment, many organizations lack continuous visibility into which services are externally exposed at any given moment. If you do not know a medical device or DICOM server is accessible from the internet, you cannot secure it. What was once ‘plug and play’ infrastructure can quietly become ‘plug and prey’.
Securing DICOM servers in healthcare
Organizations reviewing imaging system security should confirm whether Port 104 is accessible from outside trusted networks. Where external access is operationally required, it should be restricted through VPN controls and strong authentication. DICOM traffic should be encrypted where supported.
Additional steps include:
Reviewing firewall rules governing PACS and modality communication.
Conducting periodic external service discovery across owned IP ranges.
Verifying vendor default configurations during deployment and upgrade cycles.
Monitoring newly exposed services following infrastructure or cloud changes.
These measures focus on aligning network exposure with clinical intent. The objective is straightforward: Ensure that imaging systems are reachable only by the parties that need them.
Healthcare cyber resilience starts with visibility
Imaging systems play a central role in diagnosis and care planning, with operational disruption creating immediate clinical consequences.. As regulatory scrutiny of healthcare cybersecurity continues to increase, confirming that DICOM services operate within intended network boundaries is a practical and measurable step toward reducing risk.
The identification of more than 30 exposed systems highlights a visibility gap rather than a failure of awareness. Addressing that gap begins with systematic review of external-facing infrastructure and sustained monitoring over time.
Senior leaders are visible by design. They speak at events, post on LinkedIn, sit on boards, and sign public filings. That visibility builds brands and drives growth. It also creates risk.
The findings are clear: an executive’s online footprint is not just a privacy issue. It is a business risk.
Across industries, we found that surface web data, public records, social media activity, and leaked credentials combine to create a detailed profile that threat actors can weaponize. In many cases, 60% of an individual’s digital risk exposure is retrievable through a simple surface web search. When paired with breached credentials circulating in criminal forums, that information fuels business email compromise, spear phishing, impersonation, and even hybrid cyber-physical threats.
Our research features the Rapid7 Exposure Prevention (REP) Score, a quantitative metric that measures executive exposure across four areas: general exposure, social media, public records, and leaked credentials. The data reveals meaningful differences by industry and geography, with U.S.-based executives generally more exposed than their European counterparts, particularly in public records and credential leaks.
High-profile incidents continue to show how small details can lead to large-scale impact. The takeaway for security leaders is direct: protecting executives requires more than awareness training. It demands continuous monitoring, strong authentication, proactive credential hygiene, and integration between cyber and physical risk programs.
Download the Rapid7 report
Download the full report to see how your organization compares and how to reduce executive exposure before attackers take advantage.
Security teams have been talking about alert fatigue for years. And yet, for many SOCs, the problem isn’t getting better. It’s getting worse.
As environments expand across cloud, SaaS, identity, and legacy systems, analysts are flooded with signals that all demand attention but rarely arrive with enough context to act quickly. Staffing shortages only amplify the issue. The result is a SOC stuck reacting to noise instead of responding to real risk.
Recent industry research reinforces what analysts already know. False positives remain one of the top challenges in detection and response, and many analysts encounter low-value alerts so frequently that it slows investigations and contributes directly to burnout. Alert fatigue isn’t just an efficiency problem. It’s an operational risk.
Why alert fatigue persists, and why it’s not your fault
Alert fatigue isn’t a reflection of weak analysts or underperforming teams. It’s the outcome of security models that haven’t kept pace with modern complexity.
Traditional SIEM approaches were built for a different era. Rule-heavy detections, manual enrichment, siloed tools, and flat log views force analysts to spend valuable time stitching together context before they can even begin investigating. Even experienced analysts end up waiting for answers instead of acting on them.
Modern SOCs need a different approach. One that prioritizes analyst efficiency, reduces friction, and brings clarity to investigations from the start.
Four moves that change how SOCs operate
In the eBook, we break down four practical shifts that high-performing SOCs are making to move beyond alert fatigue:
Automate the noise with AI-assisted classification and enrichment so analysts can focus on what truly matters
Investigate smarter with unified context, eliminating unnecessary pivots between tools
Shrink the response cycle using guided workflows that make investigations faster and more consistent
Gain confidence in coverage by understanding risk across the entire attack surface, not just known assets
These aren’t theoretical ideas. They’re grounded in real-world SOC workflows and designed to help analysts move faster without sacrificing control or trust.
A look inside a real SOC investigation
One of the most impactful sections of the eBook walks through a familiar scenario: a phishing or business email compromise investigation.
Instead of listing tools or features, it shows what the investigation actually feels like for an analyst. From the frustration of waiting on data in a traditional workflow to the clarity that comes when context is surfaced early and answers arrive faster. It’s a reminder that efficiency isn’t about removing analysts from the loop. It’s about removing the friction that slows them down.
From overwhelmed to in command
At its core, the playbook is built on a simple principle. Modern SOC efficiency comes from reducing noise, unifying context, and guiding investigations with AI-assisted workflows, all while keeping analysts firmly in control.
If you’re responsible for detection and response, or if you’re feeling the strain of alert fatigue in your SOC, this eBook is designed for you.
We are excited to share Rapid7’s recognition in The Forrester Wave™: Cloud Native Application Protection Solutions (CNAPP), Q1 2026 [1]. We see this acknowledgment as a milestone that highlights our strategic evolution and continued drive to help security teams shift from reactive defense to proactive, preemptive response.
Threat actors today know that organizations with static, moment-in-time snapshots of their environments struggle to identify misconfigurations, overprivileged identities, and vulnerabilities in cloud environments. It’s why effective cloud security has shifted from isolated tools that lock down a single container or run a standalone scanner, to platforms that are an integral part of a broader continuous exposure management and threat detection and response (TDR) strategy.
Leading with outstanding integration
As noted, one of the most critical challenges for modern security teams is protecting their technology stacks with fragmented security tools. That’s why integrations are so important. The Forrester report states: “Rapid7’s outstanding third-party solution integration includes asset management, third-party solutions, bidirectional integration with ticketing systems, SIEM integration, and SOAR and ASPM tool integrations.”
To us, this recognition reflects our belief that by integrating deeply with remediation workflows, whether it’s automated ticketing or advanced application security posture management (ASPM), we eliminate the silos that prevent cloud security from becoming a seamless part of an organization’s security operations.
Cloud security does not live in a vacuum; security leaders need to understand the potential impact of cloud or container vulnerabilities and misconfigurations within the wider business and cybersecurity program. Security operations teams need cloud alerts with the relevant context delivered to their tools and workflows. This is why bidirectional integrations and automation are critical in modern security platforms.
From intelligence to proactive remediation
Forrester’s evaluation notes: “[Rapid7’s] solid innovation focuses on delivering a unified CNAPP [platform] that helps users protect cloud workloads using temporal intelligence and trending.”
We believe this finding underscores our ability to arm security teams with threat and business-centric context. We show how exposures and misconfigurations evolve over time. This empowers organizations to go beyond static snapshots of risk to achieve more proactive and effective remediation. At the core of this capability is our ability to deliver customers an expansive, continuous view of their attack surfaces. Whether an organization monitors their environment with Rapid7 or they utilize third-party scanners, our Command Platform ingests these findings and translates them into actionable remediation plans that set the foundation for automated mobilization.
Rapid7 delivers new cloud innovations
Since our participation in Forrester’s evaluation process for this report, we have continued to introduce several important new features and innovations. These updates support our customers’ cloud security requirements. In January 2026, we announced a strategic partnership with ARMO, the creators of Kubescape, to integrate runtime cloud and application security into the Rapid7 Exposure Command Platform.
Security teams are tired of seeing attacks only after the damage is done. By integrating ARMO’s continuous kernel-level observability (eBPF) into our platform, teams now have visibility into cloud behavior, enabling them to differentiate normal cloud activity from legitimate threats at runtime. They can then automatically terminate malicious processes or pause compromised containers to prevent lateral movement.
With Rapid7 cloud security, organizations can shift from seeing ‘potential’ risk to mitigating ‘active’ threats, fully completing the loop between preemptive security and proactive response.
[1] The Forrester Wave™: Cloud Native Application Protection Solutions (CNAPP), Q1 2026, Forrester Research, Inc., February 17, 2026.
Forrester does not endorse any company, product, brand, or service included in its research publications and does not advise any person to select the products or services of any company or brand based on the ratings included in such publications. Information is based on the best available resources. Opinions reflect judgment at the time and are subject to change. For more information, read about Forrester’s objectivity here .
The collective thoughts of the interwebz
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.