Post Syndicated from The History Guy: History Deserves to Be Remembered original https://www.youtube.com/watch?v=Ab28hKz69rY
AI-Powered Surveillance in Schools
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2026/01/ai-powered-surveillance-in-schools.html
It all sounds pretty dystopian:
Inside a white stucco building in Southern California, video cameras compare faces of passersby against a facial recognition database. Behavioral analysis AI reviews the footage for signs of violent behavior. Behind a bathroom door, a smoke detector-shaped device captures audio, listening for sounds of distress. Outside, drones stand ready to be deployed and provide intel from above, and license plate readers from $8.5 billion surveillance behemoth Flock Safety ensure the cars entering and exiting the parking lot aren’t driven by criminals.
This isn’t a high-security government facility. It’s Beverly Hills High School.
Венецуелски „поток“: 500 милиона евро изпрани през Инвестбанк
Post Syndicated from Екип на Биволъ original https://bivol.bg/venezuela-stream-investbank-canev.html
понеделник 19 януари 2026

Режимът на Мадуро е изпрал огромна сума през българската Инвестбанк. Това става ясно от постановление на СГП по преписка № 16709/2022. Според официалните данни на разследването, за периода 2017 г.…
Материалът Венецуелски „поток“: 500 милиона евро изпрани през Инвестбанк е публикуван за пръв път на Bivol!.
Kernel prepatch 6.19-rc6
Post Syndicated from corbet original https://lwn.net/Articles/1054924/
Linus has released 6.19-rc6 for testing.
“So we finally ended up with a slightly bigger rc than usual for this
“
stage in the release cycle, but it’s not _that_ big, and things still seem
quite stable and civilized.
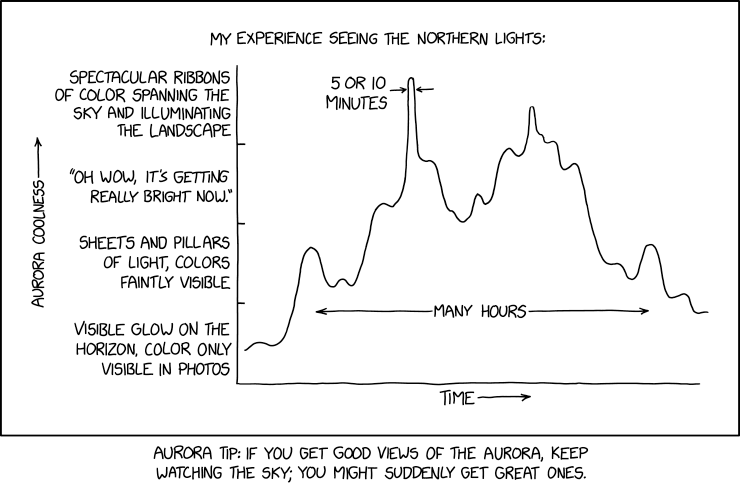
Aurora Coolness
Post Syndicated from xkcd.com original https://xkcd.com/3196/
Inside the Heffneil Christmas Lights – The HOA hates this! 🎄✨
Post Syndicated from digiblur DIY original https://www.youtube.com/watch?v=4uUDIN4uNVk
ACMER P2 33W Laser: Amazing Results… BUT Ventilation Is NOT Optional
Post Syndicated from BeardedTinker original https://www.youtube.com/watch?v=5iWFMUiQ84U
TP-Link TX201 2.5GbE PCIe Adapter Review
Post Syndicated from Rohit Kumar original https://www.servethehome.com/tp-link-tx201-2-5gbe-adapter-realtek-rtl8125/
We review the TP-Link TX201, a low-power NIC that uses a Realtek controller to add 2.5GbE to systems with free PCIe x1 ports
The post TP-Link TX201 2.5GbE PCIe Adapter Review appeared first on ServeTheHome.
Comic for 2026.01.18 – Partner
Post Syndicated from Explosm.net original https://explosm.net/comics/partner
New Cyanide and Happiness Comic
65 Essential Children’s Books
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/FFDoc5mLHno
Deja View Camwear: Odd 23-Year-Old Camera Glasses
Post Syndicated from LGR original https://www.youtube.com/watch?v=vCfvFQH_1YA
Mancy
Post Syndicated from Oglaf! -- Comics. Often dirty. original https://www.oglaf.com/mancy/

Four stable kernels for the weekend
Seagate Shipping 32TB HAMR Hard Drives for Server, NAS, & Surveillance Markets
Post Syndicated from Ryan Smith original https://www.servethehome.com/seagate-shipping-32tb-hamr-hard-drives-for-server-nas-surveillance-markets/
Seagate has announced this week that it has begun shipping 32TB versions of its high-capacity, high-end hard drives. The second wave of hard drives based on Seagate’s heat-assisted magnetic recording (HAMR) technology, the 32TB drives mark the first capacity bump for Seagate’s top-capacity drives since Seagate brought HAMR-based drives to the retail market last year. […]
The post Seagate Shipping 32TB HAMR Hard Drives for Server, NAS, & Surveillance Markets appeared first on ServeTheHome.
Sophie Gilbert on the persistence of misogyny on tech platforms
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/jB2P2ACCpTg
Нов договор с Майкрософт или търсене на алтернативи?
Post Syndicated from Bozho original https://blog.bozho.net/blog/4561
Предстои нов договор с Майкрософт за държавната администрация. На фона на централните политически събития и многото комуникационен шум, на заден план остана решението на Министерския съвет да възложи на министъра на електронното управление да проведе обществена поръчка за продукти на Майкрософт.
Преди да отворя темата за офис пакета, трябва да уточня две неща: 1) държавната администрация ползва много продукти на Microsoft, чието лицензиране и поддръжка трябва да уреди – Windows Server, SQL Server и др. Това не е офис пакета и там дори да имаме технологични спорове за Windows vs Linux и за най-удачния избор за системи за бази данни, безпорна е нуждата от поддръжка. и 2) Microsoft е компания с добра репутация и големи и компетентни партньорски мрежи, което осигурява достатъчни гаранции за администрацията, че няма да бъде оставена да се оправя сама (което тя не може).
След тези уточнения, да минем на темата с офис пакета. Microsoft от много години предлага Office365 – облачен офис, при който Word, Excel и PowerPoint продължават да работят локално, но имат и функционалности за споделяне и колаборация, които пък изискват облачна интеграция. Предлага и централизирано управление на имейл. В частния сектор съм бил клиент на Office365, и той спестява много главоболия и налага много добри практики, вкл. във връзка с киберсигурността. Имам и негативен опит с поддръжката в Индия, която един месец не можа да разбере какво ги питам и накрая си призна, че имат бъг, но нетният резултат е безспорно позитивен.
Но тук идва проблемът, с който се сблъсках като министър – Майкрософт изисква всички потребителски акаунти да бъдат в облачната активна директория (AzureAD/Entra). Това означава цялата държавна администрация (десетки хиляди служители) да бъдат управлявани в облака на Майкрософт. Друг проблем са данните – Microsoft не предлагаше на правителствата възможността да контролират изцяло ключовете за криптиране на данните, което значеше, че Microsoft на теория има достъп до всички данни.
През 2022 г. като министър, повдигнах тези въпроси като проблем за България, защото от гледна точка на националната сигурност и суверенитета, е дългосрочен риск да отдадем толкова много контрол на компания от трета страна. Оттогава Майкрософт въведоха повече възможности за криптиране на данните от правителства – през 2025 г. въведоха поддръжка за хибридни среди с държавна инфраструктура, което е стъпка в правилната посока.
На този фон, обаче, идва проблемът е международния наказателен съд в Хага. След като Тръмп санкционира съда в хага, достъпът до имейла (в Office365) на главния прокурор към съда е бил спрян. Майкрософт първо не коментира, а после отрича да са правили нещо нередно. Но каквато и да е реалната ситуация, администрацията на САЩ разполага с инструменти да наложи определени действия на американските технологични компании.
Друга история от 2022 г. – един от големите облачни доставчици (hyperscaler-и) разглеждаше възможност за партньорство с българското правителство. Бидейки наясно с вътрешния капацитет за поддържане на облачна инфраструктура, бях много отворен към хибридни модели, в които ползваме и дори насърчаваме инвестиции на hyperscaler-и в страната, съвместно с наша инфраструктура. За съжаление времето беше твърде кратко за се развие такова партньорство, но в рамките на една среща казах, че е изключително важно да има възможност за безпроблемна мгирация извън облака, поне на ниво виртуална машина, за да няма т.нар. vendor lock-in. Те ме увериха, че няма никакъв проблем с миграцията на виртуални машини, без да знаят, че предната вечер бях мигрирал такава, във връзка със спешното създаване на български сайт за украински бежанци и се беше оказало, че изобщо не е безпроблмно и има доста скрити пречки.
В този контекст, дългосрочното обвързване на държавата с външен доставчик на такива централни услуги, без възможност и подготовка за миграция в рамките на часове, е доста рисково. Както от гледна точка на достъпа до данните, така и от гледна точка на наличността на услулгата – ако някой може да спре от днес за утре достъпа до ключова услуга по политически причини, това е проблем.
Германия отдавна е осъзнала този проблем, поради което е създала Центъра за цифров суверенитет (ZenDIS), който разработва продукти, които немската администрация ползва и чрез които не зависи от външни доставчици. След гореописания инцидент, Международният наказателен съд в Хага мигрира от Office365 към openDesk на ZenDIS, който е изцяло с отворен код.
Нека горното да не се чете като обвинение към американските компании – не че нямам технологични критики към тях, но те предоставят добри продукти, които за съжаление никоя европейска компания не е успяла да развие и наложи в такава степен.
Но от гледна точка на дългосрочните рискове и на новата ситуация, в която партньорството между САЩ и Европа е поставено под въпрос от Белия дом, следва да оценяваме внимателно и технологичните си решения.
В решението на Министерския съвет е записано „или еквивалентни“, което позволява на МЕУ да разграничи поддръжката на съществуващи сървърни продукти от офис пакета и да помисли за отворени алтернативи, които да гарантират цифров суверенитет.
Материалът Нов договор с Майкрософт или търсене на алтернативи? е публикуван за пръв път на БЛОГодаря.
Седмицата (12–17 януари)
Post Syndicated from Йовко Ламбрев original https://www.toest.bg/sedmitsata-12-17-yanuari/

Едва преполовихме януари, а толкова много неща вече успяха да се случат с дата от 2026 година. Ако вече се чувствате така, сякаш сте преживели цял месец (или даже няколко месеца), това не е само ваше субективно усещане. Когато събитията връхлитат с такава честота, настоящето сякаш се компресира до миг, в който няма време за осмисляне на една новина, преди тя да бъде пометена от следващата.
И не е само времето. Дистанциите окончателно губят значението си, а икономическите и политическите трусове в различни точки на планетата резонират мигновено и едновременно в нашия дневен ред, сякаш и светът внезапно се е свил. Иран, Венецуела, Украйна, Газа, Минеаполис, Гренландия… са не твърде по-далеч от покрайнините на градовете ни и съвсем не в периферията на мислите ни.
В „Тоест“ обаче никога не се напъваме да вместим повече история в единица време, защото отдавна знаем, че това води не до по-богат опит, а до колективно задъхване и усещане, че бягаме на място, опитвайки се да догоним опашката си. Затова разглобяваме свръхнаситеното с информация ежедневие, търсейки тези парченца, които носят смисъл и имат значение за бъдещето.
А онова, което има най-голямо значение за бъдещето на всички ни тук, в България, е да разглобим и унищожим веднъж завинаги добре смазаната, но смазваща развитието на страната ни машина за избори на управляващите. Това може да стане само с невиждано и нечувано масово гласуване на предстоящите предсрочни избори. Защото иначе онези никога няма да допуснат машинно гласуване, никога няма да изпуснат контрола върху броенето, а тяхното си МВР ще продължи да си затваря очите пред изборните безобразия и купувачите на гласове. Повече по темата четете в седмичния анализ на Емилия Милчева „В броячите е силата. Не, в гражданите“.
И ето! Доживяхме и новогодишното приветствие на Е.Т. в комплект със саркастичния ѝ коментар за събитията от седмицата. Видеото съдържа нездравословни дози груба действителност. Гледайте го на своя отговорност.
Толерантни ли сме един към друг? Как мислите? Да? Не? Зависи? Адски сме толерантни!, зашеметява ни още със заглавието на статията си тази седмица Светла Енчева. За да ни довърши с анализа си на последните резултати (за 2025 г.) от ежегодното национално представително изследване на обществените нагласи спрямо ЛГБТИ хората. Е, има и някои добри новини и тенденции. Аз пък си мисля, че ако темата някой ден излезе от режима на пропагандно-политическата експлоатация, обществото ни трябва да успее да я обговори и надрасне спокойно. Дано се случи по-скоро.
С политическия си анализ тази седмица Искрен Иванов се опитва рационално да обясни последните действия на администрацията на Тръмп, които ни изглеждат откровено безумни. И безпрецедентни само на фона на днешния контекст, но не и в рамките на историческите натрупвания, които често погрешно допускаме, че са останали безвъзвратно в миналото, а може би не са. Или продължават да имат своето влияние и днес. Може да прочетете повече в статията му „Да владееш или да не владееш? Как Западът се върна към началото на XX век“.
За Тръмп и САЩ няма как да не стане дума и в новия епизод на видеопоредицата ни „Тоест разговаряме“, който ще излъчим на живо днес, 17 януари, от 16:00 часа в нашия YouTube Live. Защото събеседник на Владислав Севов ще бъде Йоанна Елми, авторка в „Тоест“ от началото на 2019 г. и водеща на рубриката „Гласовете на Америка“. В анкетата на епизода може да зададете предварителен въпрос на Йоанна и да довършите изречението „Американската мечта е…“.
Дори литературната ни колонка „На второ четене“ е уплътнена със свръхбагажа на новото трескаво ежедневие. И за съжаление – напоена с кръв. С неизбежните паралели между там и тук, тях и нас. Стефан Иванов е виновен за това – и Остап Сливински с неговия „Речник на войната“. Защото според Стефан
езикът е последното бойно поле. След като градовете са паднали, след като институциите са рухнали, след като идентичностите са разбити, остава още въпросът как ще говорим за това… Ще говорим внимателно, болезнено и честно. Ще говорим така, сякаш думите тежат. Защото тежат.
И още паралели… Този път със Сърбия, за която ни разказва италианката Джорджа Спадони в няколко статии от първо лице. Тази седмица публикувахме най-новия материал от поредицата ѝ, който е озаглавен „Какво става в Сърбия? Непредвидимото бъдеще“. Текстът завършва с констатацията, че за добро или зло друго бъдеще няма – с това разполагаме. Но го има очевидния намек, че все пак от нас зависи какво ще бъде то.
Струва ми се, че сполучливо допълнение към статията на Джорджа би било припомнянето на един кратък документален филм на вече над 20 години. Той е за един исторически импулс, изпълнен с много човешки, обикновени мечти, който сега можеше да се е превърнал в по-различно настояще, ако повече хора бяха повярвали в него и в собствените си сили за промяна.
„Няма народ, който да е направил погрешен политически избор и да не е платил цената за това“, ще чуете да казва Зоран Джинджич в този филм. Затова стига вече грешни избори!
A Romance That Actually Takes Sex Seriously
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/KC8taGfwjuM
Implementing data governance on AWS: Automation, tagging, and lifecycle strategy – Part 2
Post Syndicated from Omar Ahmed original https://aws.amazon.com/blogs/security/implementing-data-governance-on-aws-automation-tagging-and-lifecycle-strategy-part-2/
In Part 1, we explored the foundational strategy, including data classification frameworks and tagging approaches. In this post, we examine the technical implementation approach and key architectural patterns for building a governance framework.
We explore governance controls across four implementation areas, building from foundational monitoring to advanced automation. Each area builds on the previous one, so you can implement incrementally and validate as you go:
- Monitoring foundation: Begin by establishing your monitoring baseline. Set up AWS Config rules to track tag compliance across your resources, then configure Amazon CloudWatch dashboards to provide real-time visibility into your governance posture. By using this foundation, you can understand your current state before implementing enforcement controls.
- Preventive controls: Build proactive enforcement by deploying AWS Lambda functions that validate tags at resource creation time. Implement Amazon EventBridge rules to trigger real-time enforcement actions and configure service control policies (SCPs) to establish organization-wide guardrails that prevent non-compliant resource deployment.
- Automated remediation: Reduce manual intervention by setting up AWS Systems Manager Automation Documents that respond to compliance violations. Configure automated responses that correct common issues like missing tags or improper encryption and implement classification-based security controls that automatically apply appropriate protections based on data sensitivity.
- Advanced features: Extend your governance framework with sophisticated capabilities. Deploy data sovereignty controls to help ensure regulatory compliance across AWS Regions, implement intelligent lifecycle management to optimize costs while maintaining compliance, and establish comprehensive monitoring and reporting systems that provide stakeholders with clear visibility into your governance effectiveness.
Prerequisites
Before beginning implementation, ensure you have AWS Command Line Interface (AWS CLI) installed and configured with appropriate credentials for your target accounts. Set AWS Identity and Access Managment (IAM) permissions so that you can create roles, Lambda functions, and AWS Config rules. Finally, basic familiarity with AWS CloudFormation or Terraform will be helpful, because we’ll use CloudFormation throughout our examples.
Tag governance controls
Implementing tag governance requires multiple layers of controls working together across AWS services. These controls range from preventive measures that validate resources at creation to detective controls that monitor existing resources. This section describes each control type, starting with preventive controls that act as first line of defense.
Preventive controls
Preventive controls help ensure resources are properly tagged at creation time. By implementing Lambda functions triggered by AWS CloudTrail events, you can validate tags before resources are created, preventing non-compliant resources from being deployed:
For complete, production-ready implementation, see Implementing Tag Policies with AWS Organizations and EventBridge event patterns for resource monitoring.
Organization-wide policy enforcement
AWS Organizations tag policies provide a foundation for consistent tagging across your organization. These policies define standard tag formats and values, helping to ensure consistency across accounts:
Detailed implementation guidance: Getting started with tag policies & Best practices for using tag policies
Tag-based access control
Tag-based access control gives you detailed permissions using attribute-based access control (ABAC). By using this approach, you can define permissions based on resource attributes rather than creating individual IAM policies for each use case:
Multi-account governance strategy
While implementing tag governance within a single account is straightforward, most organizations operate in a multi-account environment. Implementing consistent governance across your organization requires additional controls:
For more information, see implementation guidance for SCPs.
Integration with on-premises governance frameworks
Many organizations maintain existing governance frameworks for their on-premises infrastructure. Extending these frameworks to AWS requires careful integration and applicability analysis. The following example shows how to use AWS Service Catalog to create a portfolio of AWS resources that align with your on-premises governance standards.
Automating security controls based on classification
After data is classified, use these classifications to automate security controls and use AWS Config to track and validate that resources are properly tagged through defined rules that assess your AWS resource configurations, including a built-in required-tags rule. For non-compliant resources, you can use Systems Manager to automate the remediation process.
With proper tagging in place, you can implement automated security controls using EventBridge and Lambda. By using this combination, you can create a cost-effective and scalable infrastructure for enforcing security policies based on data classification. For example, when a resource is tagged as high impact, you can use EventBridge to trigger a Lambda function to enable required security measures.
This example automation applies security controls consistently, reducing human error and maintaining compliance. Code-based controls ensure policies match your data classification.
Implementation resources:
- Remediating Noncompliant Resources with AWS Config
- AWS Systems Manager – Creating your own runbooks
- AWS Encryption SDK Developer Guide
- Lambda error handling patterns
- EventBridge event patterns
Data sovereignty and residency
Data sovereignty and residency requirements help you comply with regulations like GDPR. Such controls can be implemented to restrict data storage and processing to specific AWS Regions:
Note: This example uses eu-west-1 and eu-central-1 because these Regions are commonly used for GDPR compliance, providing data residency within the European Union. Adjust these Regions based on your specific regulatory requirements and business needs. For more information, see Meeting data residency requirements on AWS and Controls that enhance data residence protection.
Disaster recovery integration with governance controls
While organizations often focus on system availability and data recovery, maintaining governance controls during disaster recovery (DR) scenarios is important for compliance and security. To implement effective governance in your DR strategy, start by using AWS Config rules to check that DR resources maintain the same governance standards as your primary environment:
For your most critical data (classified as Level 1 in part 1 of this post), implement cross-Region replication while maintaining strict governance controls. This helps ensure that sensitive data remains protected even during failover scenarios:
Automated compliance monitoring
By combining AWS Config for resource compliance, CloudWatch for metrics and alerting, and Amazon Macie for sensitive data discovery, you can create a robust compliance monitoring framework that automatically detects and responds to compliance issues:
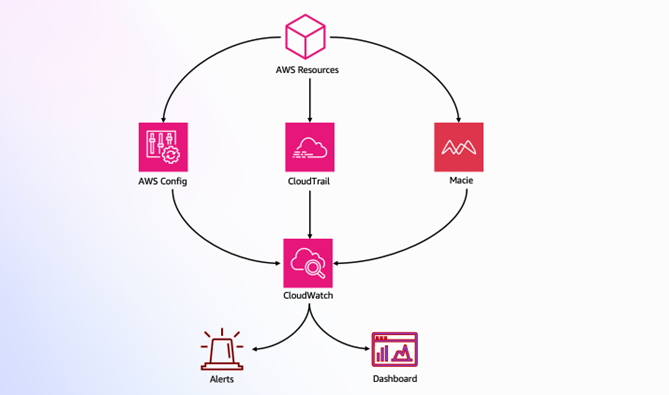
Figure 1: Compliance monitoring architecture
This architecture (shown in Figure 1) demonstrates how AWS services work together to provide compliance monitoring:
- AWS Config, CloudTrail, and Macie monitor AWS resources
- CloudWatch aggregates monitoring data
- Alerts and dashboards provide real-time visibility
The following CloudFormation template implements these controls:
These controls provide real-time visibility into your security posture, automate responses to potential security events, and use Macie for sensitive data discovery and classification. For a complete monitoring setup, review List of AWS Config Managed Rules and Using Amazon CloudWatch dashboards.
Using AWS data lakes for governance
Modern data governance strategies often use data lakes to provide centralized control and visibility. AWS provides a comprehensive solution through the Modern Data Architecture Accelerator (MDAA), which you can use to help you rapidly deploy and manage data platform architectures with built-in security and governance controls. Figure 2 shows an MDAA reference architecture.
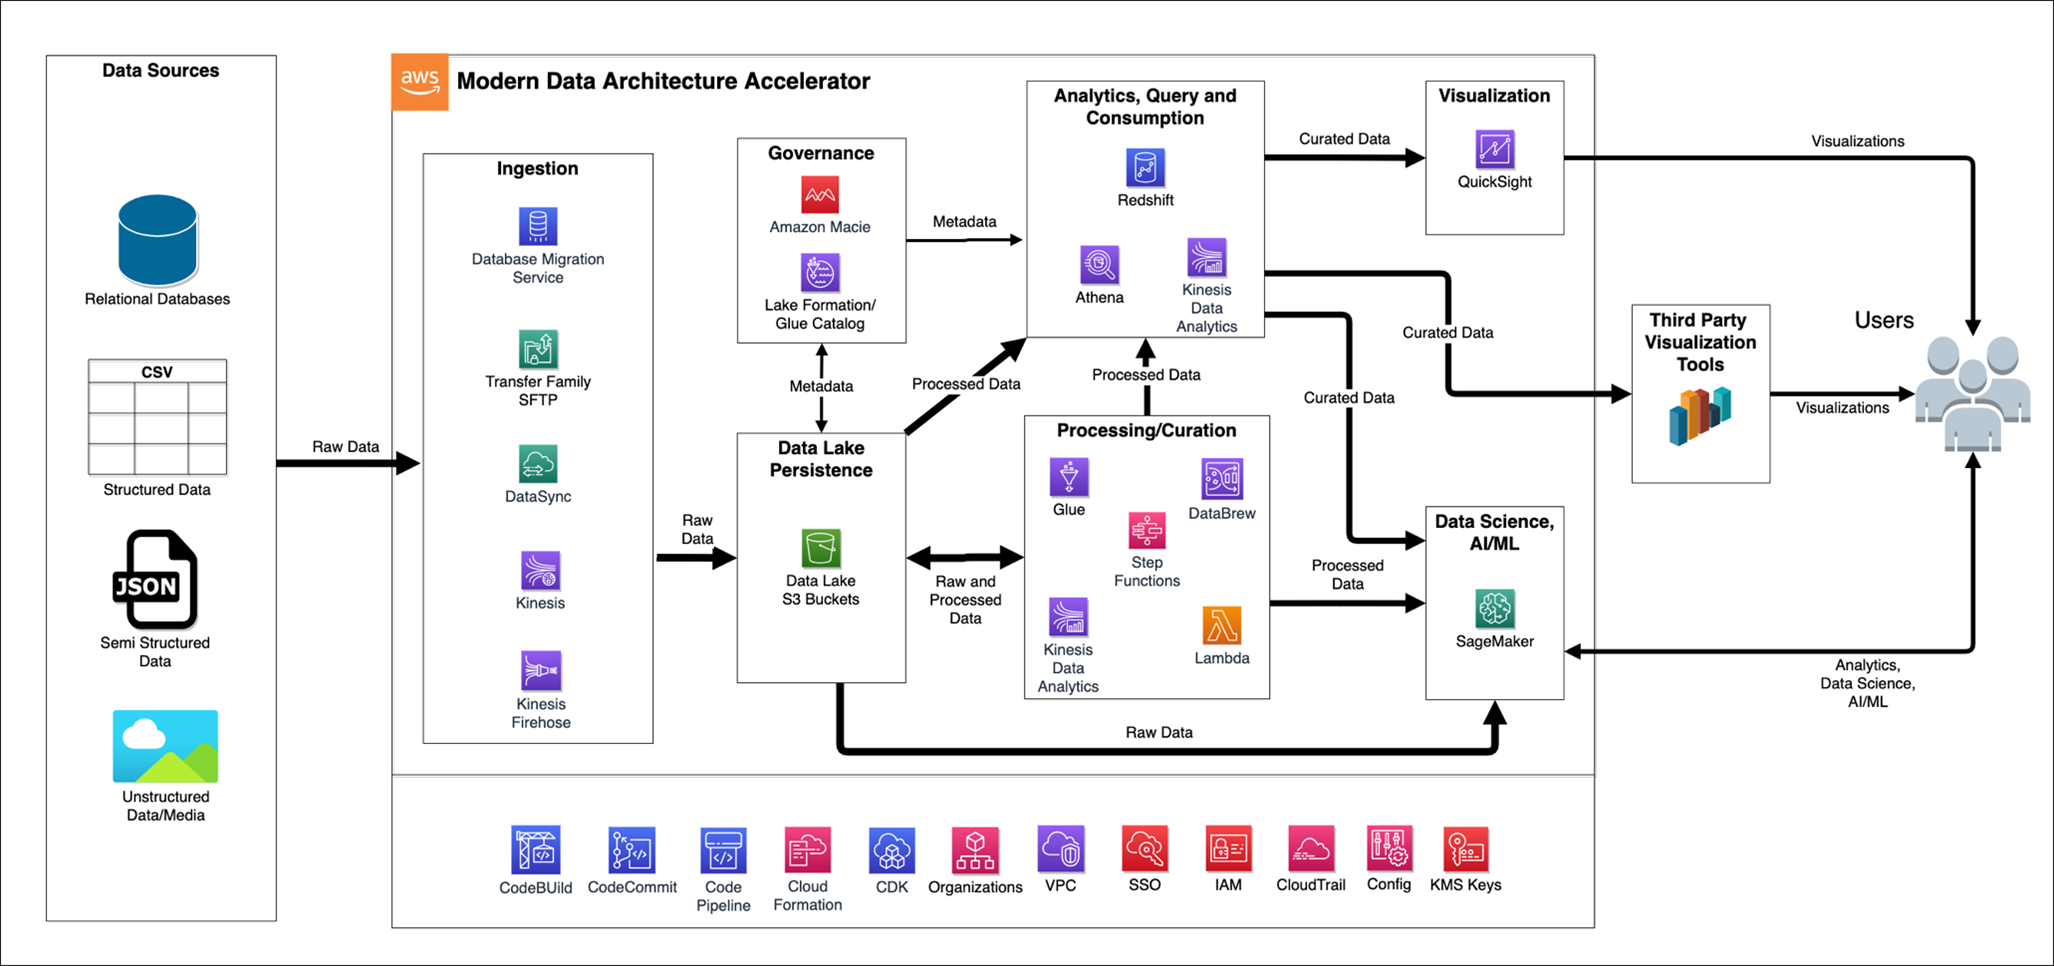
Figure 2: MDAA reference architecture
For detailed implementation guidance and source code, see Accelerate the Deployment of Secure and Compliant Modern Data Architectures for Advanced Analytics and AI.
Access patterns and data discovery
Understanding and managing access patterns is important for effective governance. Use CloudTrail and Amazon Athena to analyze access patterns:
This query helps identify frequently accessed data and unusual patterns in access behavior. These insights help you to:
- Optimize storage tiers based on access frequency
- Refine DR strategies for frequently accessed data
- Identify of potential security risks through unusual access patterns
- Fine-tune data lifecycle policies based on usage patterns
For sensitive data discovery, consider integrating Macie to automatically identify and protect PII across your data estate.
Machine learning model governance with SageMaker
As organizations advance in their data governance journey, many are deploying machine learning models in production, necessitating governance frameworks that extend to machine learning (ML) operations. Amazon SageMaker offers advanced tools that you can use to maintain governance over ML assets without impeding innovation.
SageMaker governance tools work together to provide comprehensive ML oversight:
- Role Manager provides fine-grained access control for ML roles
- Model Cards centralize documentation and lineage information
- Model Dashboard offers organization-wide visibility into deployed models
- Model Monitor automates drift detection and quality control
The following example configures SageMaker governance controls:
This example demonstrates two essential governance controls: role-based access management for secure service interactions and automated hourly monitoring for ongoing model oversight. While these technical implementations are important, remember that successful ML governance requires integration with your broader data governance framework, helping to ensure consistent controls and visibility across your entire data and analytics ecosystem. For more information, see Model governance to manage permissions and track model performance.
Cost optimization through automated lifecycle management
Effective data governance isn’t just about security—it’s also about managing cost efficiently. Implement intelligent data lifecycle management based on classification and usage patterns, as shown in Figure 3:
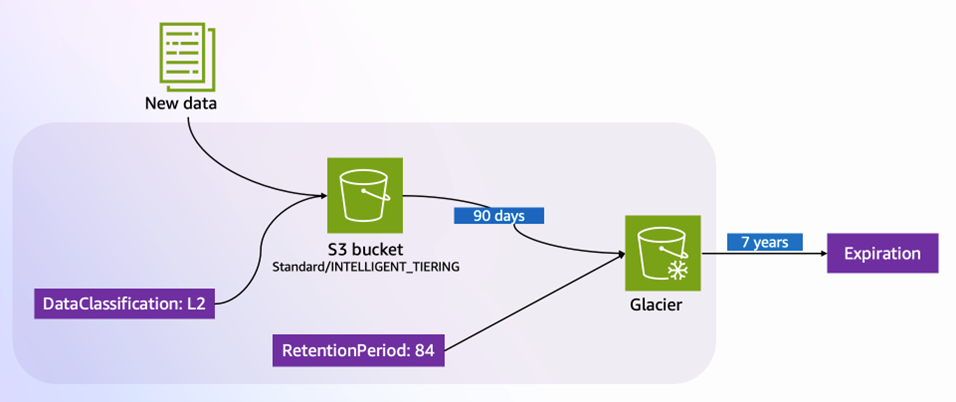
Figure 3: Tag-based lifecycle management in Amazon S3
Figure 3 illustrates how tags drive automated lifecycle management:
- New data enters Amazon Simple Storage Service (Amazon S3) with the tag
DataClassification: L2 - Based on classification, the data starts in
Standard/INTELLIGENT_TIERING - After 90 days, the data transitions to Amazon S3 Glacier storage for cost-effective archival
- The
RetentionPeriodtag (84 months) determines final expiration
Here’s the implementation of the preceding lifecycle rules:
S3 Lifecycle automatically optimizes storage costs while maintaining compliance with retention requirements. For example, data initially stored in Amazon S3 Intelligent-Tiering automatically moves to Glacier after 90 days, significantly reducing storage costs while helping to ensure data remains available when needed. For more information, seeManaging the lifecycle of objects and Managing storage costs with Amazon S3 Intelligent-Tiering.
Conclusion
Successfully implementing data governance on AWS requires both a structured approach and adherence to key best practices. As you progress through your implementation journey, keep these fundamental principles in mind:
- Start with a focused scope and gradually expand. Begin with a pilot project that addresses high-impact, low-complexity use cases. By using this approach, you can demonstrate quick wins while building experience and confidence in your governance framework.
- Make automation your foundation. Apply AWS services such as Amazon EventBridge for event-driven responses, implement automated remediation for common issues, and create self-service capabilities that balance efficiency with compliance. This automation-first approach helps ensure scalability and consistency in your governance framework.
- Maintain continuous visibility and improvement. Regular monitoring, compliance checks, and framework updates are essential for long-term success. Use feedback from your operations team to refine policies and adjust controls as your organization’s needs evolve.
Common challenges to be aware of:
- Initial resistance to change from teams used to manual processes
- Complexity in handling legacy systems and data
- Balancing security controls with operational efficiency
- Maintaining consistent governance across multiple AWS accounts and regions
For more information, implementation support, and guidance, see:
- AWS Security Blog
- AWS Architecture Center
- AWS Compliance Resources
- Amazon Macie User Guide
- AWS Organizations Best Practices
By following this approach and remaining mindful of potential challenges, you can build a robust, scalable data governance framework that grows with your organization while maintaining security, compliance, and efficient data operations.
If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, contact AWS Support.
Implementing data governance on AWS: Automation, tagging, and lifecycle strategy – Part 1
Post Syndicated from Omar Ahmed original https://aws.amazon.com/blogs/security/implementing-data-governance-on-aws-automation-tagging-and-lifecycle-strategy-part-1/
Generative AI and machine learning workloads create massive amounts of data. Organizations need data governance to manage this growth and stay compliant. While data governance isn’t a new concept, recent studies highlight a concerning gap: a Gartner study of 300 IT executives revealed that only 60% of organizations have implemented a data governance strategy, with 40% still in planning stages or uncertain where to begin. Furthermore, a 2024 MIT CDOIQ survey of 250 chief data officers (CDOs) found that only 45% identify data governance as a top priority.
Although most businesses recognize the importance of data governance strategies, regular evaluation is important to ensure these strategies evolve with changing business needs, industry requirements, and emerging technologies. In this post, we show you a practical, automation-first approach to implementing data governance on Amazon Web Services (AWS) through a strategic and architectural guide—whether you’re starting at the beginning or improving an existing framework.
In this two-part series, we explore how to build a data governance framework on AWS that’s both practical and scalable. Our approach aligns with what AWS has identified as the core benefits of data governance:
- Classify data consistently and automate controls to improve quality
- Give teams secure access to the data they need
- Monitor compliance automatically and catch issues early
In this post, we cover strategy, classification framework, and tagging governance—the foundation you need to get started. If you don’t already have a governance strategy, we provide a high-level overview of AWS tools and services to help you get started. If you have a data governance strategy, the information in this post can assist you in evaluating its effectiveness and understanding how data governance is evolving with new technologies.
In Part 2, we explore the technical architecture and implementation patterns with conceptual code examples, and throughout both parts, you’ll find links to production-ready AWS resources for detailed implementation.
Prerequisites
Before implementing data governance on AWS, you need the right AWS setup and buy-in from your teams.
Technical foundation
Start with a well-structured AWS Organizations setup for centralized management. Make sure AWS CloudTrail and AWS Config are enabled across accounts—you’ll need these for monitoring and auditing. Your AWS Identity and Access Management (IAM) framework should already define roles and permissions clearly.
Beyond these services, you’ll use several AWS tools for automation and enforcement. The AWS service quick reference table that follows lists everything used throughout this guide.
Organizational readiness
Successful implementation of data governance requires clear organizational alignment and preparation across multiple dimensions.
- Define roles and responsibilities. Data owners classify data and approve access requests. Your platform team handles AWS infrastructure and builds automation, while security teams set controls and monitor compliance. Application teams then implement these standards in their daily workflows.
- Document your compliance requirements. List the regulations you must follow—GDPR, PCI-DSS, SOX, HIPAA, or others. Create a data classification framework that aligns with your business risk. Document your tagging standards and naming conventions so everyone follows the same approach.
- Plan for change management. Get executive support from leaders who understand why governance matters. Start with pilot projects to demonstrate value before rolling out organization-wide. Provide role-based training and maintain up-to-date governance playbooks. Establish feedback mechanisms so teams can report issues and suggest improvements.
Key performance indicators (KPIs) to monitor
To measure the effectiveness of your data governance implementation, track the following essential metrics and their target objectives.
- Resource tagging compliance: Aim for 95%, measured through AWS Config rules with weekly monitoring, focusing on critical resources and sensitive data classifications.
- Mean time to respond to compliance issues: Target less than 24 hours for critical issues. Tracked using CloudWatch metrics with automated alerting for high-priority non-compliance events
- Reduction in manual governance tasks: Target reduction of 40% in the first year. Measured through automated workflow adoption and remediation success rates.
- Storage cost optimization based on data classification: Target 15–20% reduction through intelligent tiering and lifecycle policies, monitored monthly by classification level.
With these technical and organizational foundations in place, you’re ready to implement a sustainable data governance framework.
AWS services used in this guide – Quick reference
This implementation uses the following AWS services. Some are prerequisites, while others are introduced throughout the guide.
|
Category |
Services |
Description |
|
Foundation |
Multi-account management structure that enables centralized policy enforcement and governance across your entire AWS environment. |
|
|
|
Controls who can access what resources through roles, policies, and permissions—the foundation of your security model. |
|
|
Monitoring and auditing |
Records every API call made in your AWS accounts, creating a complete audit trail of who did what, when, and from where. |
|
|
|
Continuously monitors resource configurations and evaluates them against rules you define (such as requiring that all S3 buckets much be encrypted). When it finds resources that don’t meet your rules, it flags them as non-compliant so you can fix them manually or automatically. |
|
|
|
Aggregates metrics, logs, and events from across AWS for real-time monitoring, dashboards, and automated alerting on governance non-compliance. |
|
|
Automation and enforcement |
Acts as a central notification system that watches for specific events in your AWS environment (such as when an S3 bucket has been created) and automatically triggers actions in response (such as by running a Lambda function to check if it has the required tags). Think of it as an if this happens, then do that automation engine. |
|
|
|
Runs your governance code (tag validation, security controls, remediation) in response to events without managing servers. |
|
|
|
Automates operational tasks across your AWS resources. In governance, it’s primarily used to automatically fix non-compliant resources—for example, if AWS Config detects an unencrypted database, Systems Manager can run a pre-defined script to enable encryption without manual intervention. |
|
|
Data protection |
Uses machine learning to automatically discover, classify, and protect sensitive data like personal identifiable information (PII) across your S3 buckets. |
|
|
|
Manages encryption keys for protecting data at rest, essential for high-impact data classifications. |
|
|
Analytics & Insights |
Serverless query service that analyzes data in Amazon S3 using SQL—perfect for querying CloudTrail logs to understand access patterns. |
|
|
Standardization |
Creates catalogs of pre-approved, governance-compliant resources that teams can deploy through self-service. |
|
|
ML Governance |
Provides specialized tools for governing machine learning operations including model monitoring, documentation, and access control. |
Understanding the data governance challenge
Organizations face complex data management challenges, from maintaining consistent data classification to ensuring regulatory compliance across their environments. Your strategy should maintain security, ensure compliance, and enable business agility through automation. While this journey can be complex, breaking it down into manageable components makes it achievable.
The foundation: Data classification framework
Data classification is a foundational step in cybersecurity risk management and data governance strategies. Organizations should use data classification to determine appropriate safeguards for sensitive or critical data based on their protection requirements. Following the NIST (National Institute of Standards and Technology) framework, data can be categorized based on the potential impact to confidentiality, integrity, and availability of information systems:
- High impact: Severe or catastrophic adverse effect on organizational operations, assets, or individuals
- Moderate impact: Serious adverse effect on organizational operations, assets, or individuals
- Low impact: Limited adverse effect on organizational operations, assets, or individuals
Before implementing controls, establishing a clear data classification framework is essential. This framework serves as the backbone of your security controls, access policies, and automation strategies. The following is an example of how a company subject to the Payment Card Industry Data Security Standard (PCI-DSS) might classify data:
- Level 1 – Most sensitive data:
- Examples: Financial transaction records, customer PCI data, intellectual property
- Security controls: Encryption at rest and in transit, strict access controls, comprehensive audit logging
- Level 2 – Internal use data:
- Examples: Internal documentation, proprietary business information, development code
- Security controls: Standard encryption, role-based access control
- Level 3 – Public data:
- Examples: Marketing materials, public documentation, press releases
- Security controls: Integrity checks, version, control
To help with data classification and tagging, AWS created AWS Resource Groups, a service that you can use to organize AWS resources into groups using criteria that you define as tags. If you’re using multiple AWS accounts across your organization, AWS Organizations supports tag policies, which you can use to standardize the tags attached to the AWS resources in an organization’s account. The workflow for using tagging is shown in Figure 1. For more information, see Guidance for Tagging on AWS.
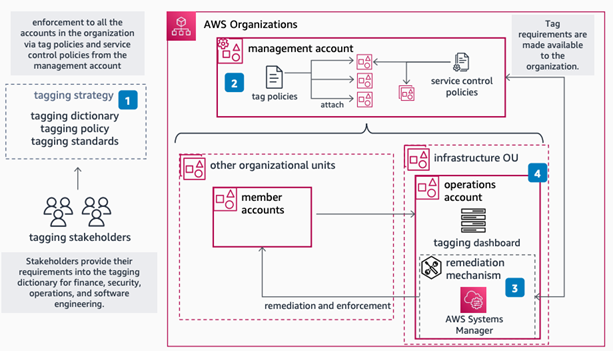
Figure 1: Workflow for tagging on AWS for a multi-account environment
Your tag governance strategy
A well-designed tagging strategy is fundamental to automated governance. Tags not only help organize resources but also enable automated security controls, cost allocation, and compliance monitoring.
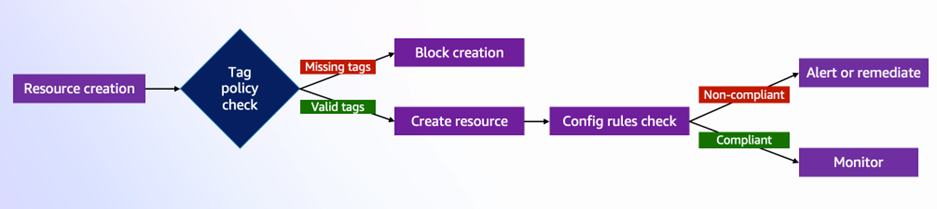
Figure 2: Tag governance workflow
As shown in Figure 2, tag policies use the following process:
- AWS validates tags when you create resources.
- Non-compliant resources trigger automatic remediation, while compliant resources deploy normally.
- Continuous monitoring catches variation from your policies.
The following tagging strategy enables automation:
While AWS Organizations tag policies provide a foundation for consistent tagging, comprehensive tag governance requires additional enforcement mechanisms, which we explore in detail in Part 2.
Conclusion
This first part of the two-part series established the foundational elements of implementing data governance on AWS, covering data classification frameworks, effective tagging strategies, and organizational alignment requirements. These fundamentals serve as building blocks for scalable and automated governance approaches. Part 2 focuses on technical implementation and architectural patterns, including monitoring foundations, preventive controls, and automated remediation. The discussion extends to tag-based security controls, compliance monitoring automation, and governance integration with disaster recovery strategies. Additional topics include data sovereignty controls and machine learning model governance with Amazon SageMaker, supported by AWS implementation examples.
If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, contact AWS Support.