Tag Archives: UK

Supporting a technical AI-focused qualification for young people in England

Post Syndicated from Diane Dowling original https://www.raspberrypi.org/blog/support-for-ai-focused-qualification-young-people-england/

Young people see and use artificial intelligence (AI) systems frequently, and hear a lot about how they are applied across many areas of life. That makes them understandably eager to find out more about how AI works. For some, this interest extends to wanting to experiment with the technology to investigate their own questions and build something themselves. How can schools support learners who want to take their interest further and gain recognition for the knowledge and skills they develop along the way?
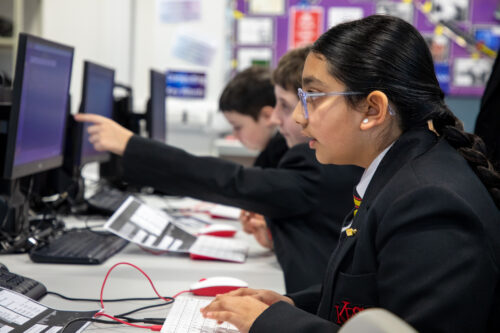
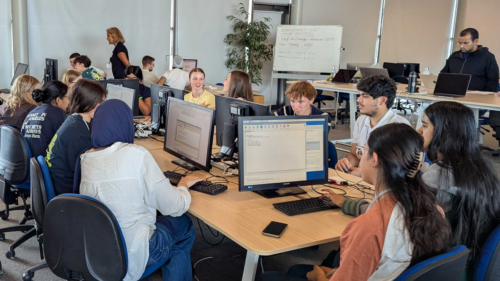
Computer science students at a desktop computer in a classroom.

For learners in the UK, there is currently no established qualification that develops technical AI skills. This can make it difficult to create space in the curriculum for dedicated AI learning, especially for learners from age 14, for whom preparation for high-stakes exams is prioritised over non-examined learning.

We have been working over the past year to develop a research-informed curriculum framework for data science, which lays out many of the foundational skills and knowledge needed to understand and develop AI models. Alongside this, we have been making the case in England for a Level 3 qualification in data science and AI. However, establishing a new qualification can take years.

In the meantime, we are starting to support students in England who choose an established route for extending their skills and getting that effort recognised: the Extended Project Qualification (EPQ).

An established qualification with room to explore AI

The EPQ is a well-established qualification for 16- to 19-year-olds offered in England, Northern Ireland, and Wales by several exam boards (including AQA, Pearson Edexcel, OCR, Eduqas/WJEC, and City & Guilds). It is completed by around 1 in 10 learners at this stage of education.

Learners pursuing an EPQ undertake an extended, self-directed investigation or project. They choose an area of interest where they want to develop their own project and take responsibility for planning, completing, and evaluating the project work.
A teenager learning computer science.

Its self-directed nature makes the EPQ particularly well suited to learners who want to explore emerging areas, such as artificial intelligence and data science. For students fascinated by AI, an EPQ offers an opportunity to do more than simply learn about the technology. With the right foundations and support, they can investigate a question of their own, build a machine learning model, and use that work to gain a recognised qualification.

We are now working to offer those foundations through a new introductory ‘Data Science and AI’ course that will enable learners to build a machine learning model as their EPQ artefact.

Building the foundations for an independent AI investigation

Creating a machine learning model involves much more than choosing a statistical technique and using easily available training data. It involves understanding the problem being addressed, deciding what data to use, exploring and preparing that data, building and evaluating a model, and interpreting the model’s outputs.

Learners who want to do this work for their EPQ need not only technical knowledge and skills, but also skills for critical thinking, research, decision-making, evaluation, and reflection — skills that are valuable for any further study and future career.
To help learners develop these foundations, we are creating an introductory ‘Data Science and AI’ course, based on our curriculum framework for data science and designed to be completed before learners begin their AI-focused EPQ.

The course will guide students through a structured investigation based on a recognised data science lifecycle. By working through it, students will:

  • Learn about each stage of the data science lifecycle
  • Develop the technical understanding they need to make independent decisions during an AI investigation 
  • Gain practical experience of working with data and building a machine learning model
  • Learn about key concepts behind the techniques they use, through theoretical content that supports them to understand not just what to do, but why

The course will consist of 10 units, each involving 2 to 3 hours of independent study for learners. We are designing the activities with a no-code approach to allow students to focus on understanding data science concepts and processes.

Supporting independent project work

Importantly, the work learners produce during this course won’t be the EPQ investigation itself. Working through ‘Data Science and AI’ will give learners the knowledge and skills they need to undertake an AI-focused project with greater independence and confidence.
A young person in a university computing classroom.

After they have completed the course, when they begin their EPQ project pursuing a question that interests them, students can apply their new skills and knowledge to make decisions about their AI investigation and document their progress.

We are looking forward to supporting learners in England to turn their interest in one of today’s most significant technologies into the opportunity to develop independent research and project skills through a recognised qualification.

What’s next?

The ‘Data Science and AI’ course will be available to selected schools in England from September 2026, where students and teachers will test the materials and we will learn from their feedback to improve the course materials. We plan to make the course freely available in 2027. 

The post Supporting a technical AI-focused qualification for young people in England appeared first on Raspberry Pi Foundation.
Supporting an AI-focused qualification for young people in England

Post Syndicated from Diane Dowling original https://www.raspberrypi.org/blog/support-for-ai-focused-qualification-young-people-england/

Young people see and use artificial intelligence (AI) systems frequently, and hear a lot about how they are applied across many areas of life. That makes them understandably eager to find out more about how AI works. For some, this interest extends to wanting to experiment with the technology to investigate their own questions and build something themselves. How can schools support students who want to take their interest further and gain recognition for the knowledge and skills they develop along the way?

Computer science students at a desktop computer in a classroom.

Currently, there is no widely available subject qualification in AI for students in the UK. This can make it difficult to create space in the curriculum for dedicated AI learning, especially for students from age 14, for whom preparation for high-stakes exams is prioritised over non-examined learning.

We have been working over the past year to develop a research-informed curriculum framework for data science, which lays out many of the foundational skills and knowledge needed to understand and develop AI models. Alongside this, we have been making the case in England for a Level 3 qualification in data science and AI. However, establishing a new qualification can take years.

In the meantime, we are starting to support students in England who choose an established route for extending their skills and getting that effort recognised: the Extended Project Qualification (EPQ).

An established qualification with room to explore AI

The EPQ is a well-established qualification for 16- to 19-year-olds offered in England, Northern Ireland, and Wales by several exam boards (including AQA, Pearson Edexcel, OCR, Eduqas/WJEC, and City & Guilds). It is completed by around 1 in 10 learners at this stage of education.

Learners pursuing an EPQ undertake an extended, self-directed investigation or project. They choose an area of interest where they want to develop their own project and take responsibility for planning, completing, and evaluating the project work.

A teenager learning computer science.

Its self-directed nature makes the EPQ particularly well suited to learners who want to explore emerging areas, such as artificial intelligence and data science. For students fascinated by AI, an EPQ offers an opportunity to do more than simply learn about the technology. With the right foundations and support, they can investigate a question of their own, build a machine learning model, and use that work to gain a recognised qualification.

We are now working to offer those foundations through a new introductory ‘Data Science and AI’ course that will enable learners to build a machine learning (ML) model as their EPQ artefact.

Building the foundations for an independent AI investigation

Creating an ML model involves much more than choosing a statistical technique and using easily available training data. It involves understanding the problem being addressed, deciding what data to use, exploring and preparing that data, building and evaluating a model, and interpreting the model’s outputs.

Learners who want to do this work for their EPQ need not only technical knowledge and skills, but also skills for critical thinking, research, decision-making, evaluation, and reflection — skills that are valuable for any further study and future career.

To help learners develop these foundations, we are creating an introductory ‘Data Science and AI’ course, based on our curriculum framework for data science and designed to be completed before learners begin their AI-focused EPQ.

The course will guide students through a structured investigation based on a recognised data science lifecycle. By working through it, students will:

  • Learn about each stage of the data science lifecycle
  • Develop the technical understanding they need to make independent decisions during an AI investigation 
  • Gain practical experience of working with data and building a machine learning model
  • Learn about key concepts behind the techniques they use, through theoretical content that supports them to understand not just what to do, but why

The course will consist of 10 units, each involving 2 to 3 hours of independent study for learners. We are designing the activities with a no-code approach to allow students to focus on understanding data science concepts and processes.

Supporting independent project work

Importantly, the work learners produce during this course won’t be the EPQ investigation itself. Working through ‘Data Science and AI’ will give learners the knowledge and skills they need to undertake an AI-focused project with greater independence and confidence.

A young person in a university computing classroom.

After they have completed the course, when they begin their EPQ project pursuing a question that interests them, students can apply their new skills and knowledge to make decisions about their AI investigation and document their progress.

We are looking forward to supporting learners in England to turn their interest in one of today’s most significant technologies into the opportunity to develop independent research and project skills through a recognised qualification.

What’s next?

The ‘Data Science and AI’ course will be available to selected schools in England from September 2026, where students and teachers will test the materials and we will learn from their feedback to improve the course materials. We plan to make the course freely available in 2027. 

The post Supporting an AI-focused qualification for young people in England appeared first on Raspberry Pi Foundation.
Robots, games, AI, and more at Coolest Projects UK 2026

Post Syndicated from Sophie Ashford original https://www.raspberrypi.org/blog/robots-games-ai-and-more-at-coolest-projects-uk-2026/

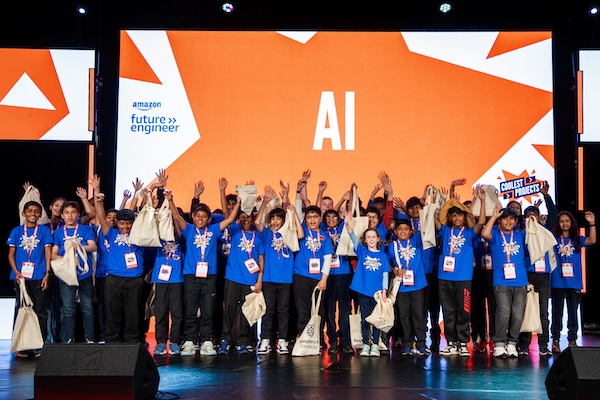
Coolest Projects UK returned to Bradford in May, with more than 200 young people showcasing digital projects they had designed and built themselves.

Visitors at the showcase event had the chance to explore an amazing range of projects across categories, from Scratch and Python to AI, hardware, web design, and game development. Every participant had the opportunity to speak with judges and industry professionals, receive personalised feedback, and connect with other young people passionate about technology and creativity. 

Throughout the day, participants also got stuck into hands-on digital activities designed to encourage collaboration and creative thinking.

A showcase built by young people

This year’s creators came from a wide range of backgrounds, including Code Clubs, schools, Scout groups, CoderDojos, and independent learning environments. Some had spent months refining their projects, while others had only recently started their coding journey. What connected them all was a shared excitement for creating with technology.

Ahead of the event, local workshops held in Bradford gave young people additional opportunities to explore digital making, develop project ideas, and gain confidence ahead of showcasing their work publicly. These sessions helped many first-time participants take their first steps into coding and creative technology.

Scouts level up their skills at a hands-on digital making workshop

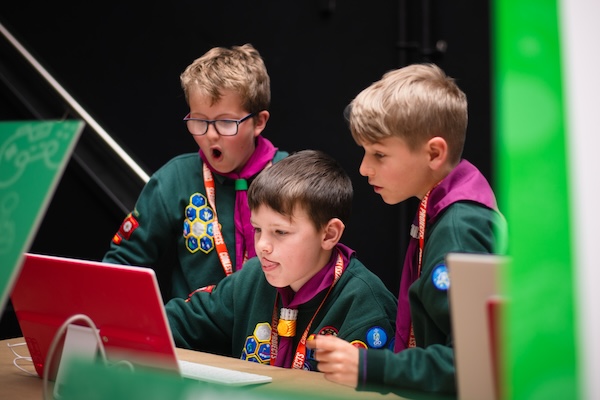
A key part of this year’s event was the involvement of 57 Scouts from across the region. Young people from six Yorkshire-based Scout groups attended digital making workshops. During the sessions, they learned how to create their own selfie filters using Scratch’s AI-facial recognition tools, earning their DM1 Digital Maker badges. After developing their own ideas and projects during the workshops, they exhibited a selection of them in the Coolest Projects showcase alongside the wider community of young creators.

For many of the Scouts attending, this was their first experience of presenting a technology project to the public. It gave them a fantastic opportunity to build confidence, talk about their ideas, and see how digital making turns imagination into reality.

Scouts at Coolest Projects UK

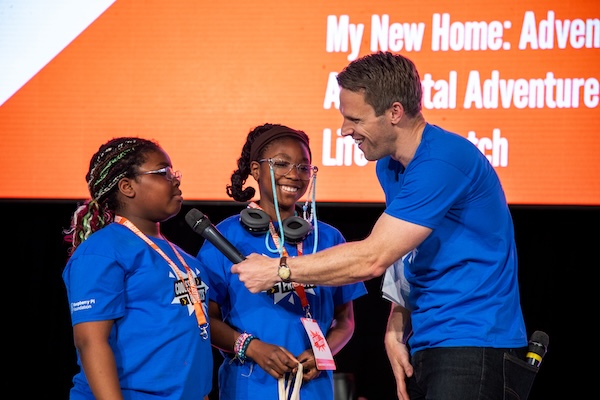
Throughout the event, Greg Foot, BBC science presenter, brought energy and enthusiasm to the stage, interviewing creators, celebrating achievements, and highlighting the stories behind the projects on display. The day concluded with a celebration ceremony where every participant received recognition for their work, with creators of the judges’ favourite projects also receiving additional awards.

The showcase featured an inspiring range of ideas and inventions created by young people from across the UK. Here are just a few of the projects presented during the event:

Seth | Pop Bot, Hardware

This project is a robotic reminder system that recognises people’s faces and plays a personalised reminder message. Using sensors, lights, sounds, and moving parts, the robot reacts when someone comes close and activates a camera for face recognition. Seth built the robot using boxes and tubes, while also using AI face recognition and recorded audio messages to create an interactive experience. Seth shared some of the challenges he faced with the facial recognition system.

“Our facial recognition system kept getting confused, so we took more photos to help it recognise better. We used different backgrounds, clothes and lighting to help it recognise our faces better, but we also took new photos when we got to Coolest Projects, so it would work better in front of the judges.”

Seth wasn’t just excited to share his project with his fellow creators, but with host Greg Foot too, bringing a little surprise along for Greg on the day.

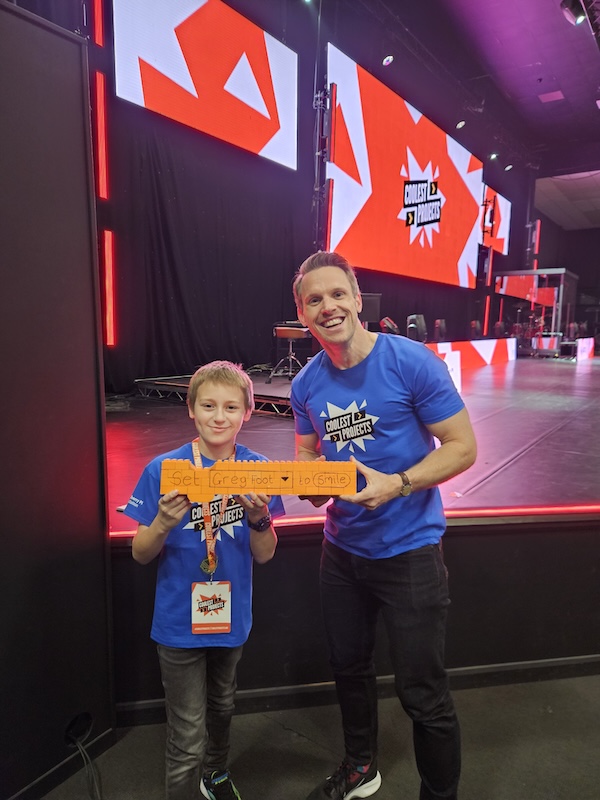
“I have always wanted to go to an event which has lots of people and showcases everyone’s work, and wanted to meet Greg Foot too. I built a giant Scratch block made from Duplo and Lego to give to Greg Foot. I didn’t have all the right sizes so I made a custom part with modelling clay and I reinforced it using sticky back plastic, then I asked my mum to write on it so that it looked like it coded Greg to smile.”

Seth at Coolest Projects UK with Greg Foot

Chinemerem | Immune System Defence, Games

Immune System Defence is a Roblox game where players protect the human heart from waves of incoming viruses. Using white blood cells, vitamin boosts and other defensive towers, players must stop the spread of infection while learning about how the immune system works. The game is designed to be both fun and educational, combining strategy and science in an exciting gameplay experience.

Chinemerem'S Immune System Defence game at Coolest Projects UK

“I got the idea for the project from my Science lessons at school — specifically the ones where we’d learned the parts of blood and the functions of the heart as a related topic on how white blood cells and the immune system protects the body. One of my favourite parts was seeing people scan my QR code and actually play my game live during the showcase.”

Gabriel | Fossil Roulette, Scratch

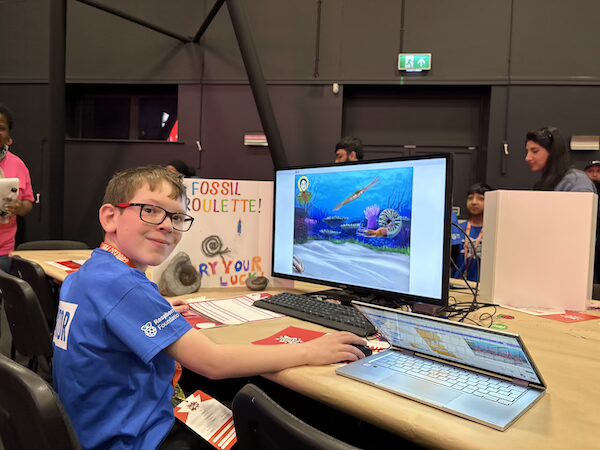
Gabriel created a Scratch game that teaches players how rare the fossilisation process is. Players choose between an ammonite, belemnite, or trilobite and then spin three roulette wheels representing different stages of fossilisation. Gabriel was inspired by a board game he saw at the Fossil Festival in Lyme Regis and adapted the idea into his own interactive game with new features such as the roulette wheels.

Gabriel at Coolest Projects UK

“The roulette wheel was the hardest to code because I had to make it spin faster at the beginning and then slow down. I found the event [Coolest Projects] very exciting because at one point I had a queue of people wanting to try out my game!”

More Coolest Projects showcases

Each year, Coolest Projects highlights the creativity, curiosity, and technical skills young people bring to digital making. From games and AI experiments to interactive hardware builds, the event continues to inspire more young people to see themselves as creators of technology, not just consumers of it.

While the UK event has now wrapped up for 2026, Coolest Projects showcases continue around the world throughout the year.

Keep creating with Code Club

Coolest Projects is part of our wider work to help every young person gain access to computing and digital creativity opportunities. At thousands of free Code Clubs running across the UK, Ireland, and around the world, young people can continue building projects, learning new skills, and creating alongside others in supportive community spaces.

To find a local club or learn how to volunteer, visit the Code Club website.

The post Robots, games, AI, and more at Coolest Projects UK 2026 appeared first on Raspberry Pi Foundation.
Enhancing your enrichment offer? Code Club is the answer

Post Syndicated from John McAtominey original https://www.raspberrypi.org/blog/code-club-enrichment-offer-schools-free-support/

There’s something really special about a Code Club. It’s a unique space for young people to get creative with technology on their terms, explore what interests them, and learn through experimenting and having fun. But speak to any Code Club leader and they’ll tell you: Code Club delivers so much more than just coding skills.

Two young people work together at a Code Club.

In the thousands of free Code Clubs across the world, you’ll see young people not only make amazing tech creations, but also grow as people. You’ll see young people find their voice and grow in confidence as they present what they’ve made to a room full of friends and parents. You’ll see them show a problem in their code to their friends and work as a team to fix it. You’ll see young people come up with the most creative digital solutions to challenges they see around them.

The ideal enrichment activity for the age of AI

We’re delighted that the UK government recently recognised Code Club as a key resource to help schools enhance their enrichment offer. This confirms what the community tells us, and what independent research shows: that Code Club works. Not only does it help young people develop their programming skills, but it also builds life skills including confidence, resilience, and problem solving. And Code Club is completely free. Schools, libraries, and community centres can set up Code Clubs using their existing equipment, and register their clubs to access all our free resources and support for getting started and running successful club sessions for the long term.

A Code Club session in a school classroom filled with young people working together at laptops.

And what about AI? There’s no getting around it, at the moment AI dominates almost every conversation about computing education, and this includes enrichment and non-formal activities too. All young people should have the power and agency to understand, question, and shape the AI systems increasingly affecting their lives. We believe that kids still need to learn to code in the age of AI, and we’ve created resources and coding projects for Code Clubs that help young people understand how AI tools work, and how to use them carefully. 

A Code Club in every UK school and library

Last year we announced our ambition to support every school and library in the UK to set up a free Code Club so that young people can develop the skills and knowledge they need to thrive in the age of AI.

Two young people smiling whilst working on their laptop with an adult mentor by their side.

Now we’re pleased to announce a package of free support for UK trusts and local authorities that are interested in becoming growth partners and setting up Code Clubs across their networks. If you join us as a growth partner, you will get:

  • Direct support from a member of our team, who will work with you to get new Code Clubs running
  • Training for your team on how to run a great Code Club experience
  • Exclusive partner logos to use on your website and in social media posts
  • Resources to promote and celebrate your clubs
  • The chance to be included in our global communications
  • Priority places at our community events
  • Access to a digital platform to monitor and manage your clubs
  • A welcome pack including some of our most popular resources
  • And of course, easy-to-follow projects for your young people

If you would like to find out more about how Code Club can enhance your enrichment offer, how easy it is to get started, and how we can help, please get in touch!

The post Enhancing your enrichment offer? Code Club is the answer appeared first on Raspberry Pi Foundation.
What students and teachers in England want from a computing curriculum

Post Syndicated from Rachel Arthur original https://www.raspberrypi.org/blog/what-students-and-teachers-in-england-want-from-a-computing-curriculum/

The UK Government is undertaking the first major review of England’s curriculum and qualifications system since the current national curriculum was introduced in 2014. We believe that this is an excellent opportunity not simply to update the computing curriculum content, but to reconsider what computing education is for, who it serves, and how it prepares young people for life in a digital society.

Today, we are launching a report featuring 6 key priorities for curriculum reform based on discussions we have had with students and teachers. 

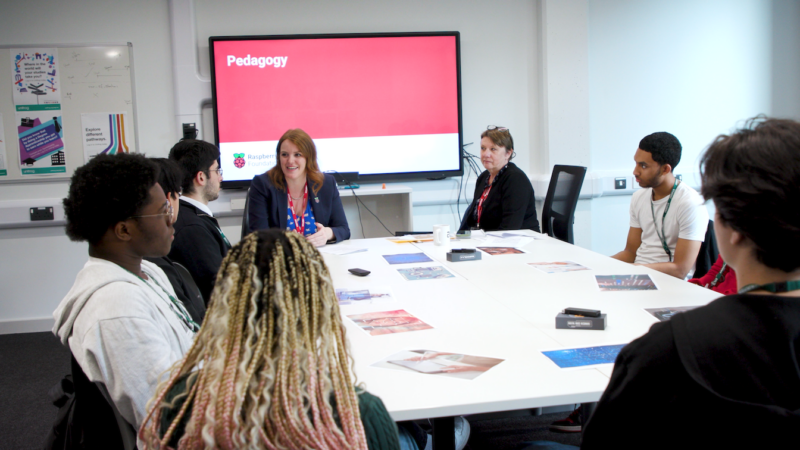
Students and educators sit at a table discussing England's curriculum review and The Future of England's Computing Curriculum.

Putting students and teachers at the heart of the conversation 

Too often, curriculum reform happens around students and teachers rather than with them. Yet these are the people who experience computing education every day, and they have valuable insights into what is working, what is not, and what needs to change. 

Our new report is based on a series of student focus groups and teacher workshops held by us and the University of Cambridge in Manchester, London, and Cambridge during spring 2026.

Teachers sit at a table discussing England's curriculum review and The Future of England's Computing Curriculum.

The student discussions included young people currently studying computer science at GCSE and A level (ages 14–18), as well as young people who had decided to not continue with the subject. We also brought together 18 computing teachers from secondary schools across England to explore curriculum priorities and challenges for implementation. 

Although participants in our workshops had differing perspectives, they consistently pointed to the same underlying challenge: the current curriculum no longer reflects the realities of technology, work, or young people’s lives. 

“AI is everywhere now, we need to understand how it works, not just be told not to use it.”
– Student, London

In particular, many students highlighted a lack of confidence in their practical digital skills despite using technology constantly in everyday life.

“I can code a bit, but I don’t know how to use Excel properly, that’s what I’ll actually need.”
– Student, London

Calls for a practical, relevant, inclusive, and future-facing curriculum

Students and teachers are not calling for a less rigorous curriculum. Nor are they arguing that computing should lose its technical foundations, with teachers consistently emphasising the value of understanding computational thinking, programming, algorithms, data, and computer systems and networks.

Instead, students and teachers want to make computing education more practical, relevant, inclusive, and future-facing.

Teachers sit at a table discussing England's curriculum review and The Future of England's Computing Curriculum.

Teachers particularly emphasised the importance of helping students understand how AI systems function, including issues such as bias, training data, limitations, and ethical implications. Participants argued that computing education should help young people understand the technologies shaping their lives, not simply prepare them for examinations. Perhaps the strongest area of agreement was that curriculum reform will only succeed if it is matched by investment in teaching.

Six key priorities for curriculum reform 

Based on our discussions with students and teachers, we have identified several priorities for curriculum reform.

1. Guarantee a core digital education for every young person

All students should leave school with a strong foundation in digital literacy, online safety, data awareness, and AI literacy. These should be treated as essential components of modern education, not optional extras.

2. Modernise curriculum content

The curriculum should focus on contemporary technologies and concepts, including AI, cybersecurity, and data, while trimming content that is overly specific, outdated, or disconnected from modern practice. Foundations such as programming, algorithms, and computational thinking should remain central.

3. Prioritise practical and applied learning

Computing should be taught through making, experimentation, and problem solving. Project-based learning, physical computing, and relevant, real-world applications should become central approaches across all ages.

4. Introduce greater flexibility and specialisation

The revised curriculum should balance a shared foundation with opportunities for students to specialise in areas aligned with their interests and aspirations.

5. Embed inclusion throughout the curriculum

Any reforms should actively address barriers to participation by ensuring inclusive teaching approaches, diverse, relatable role models, and accessible learning experiences.

6. Invest in teachers and implementation

Curriculum reform must be accompanied by sustained investment in teacher recruitment, professional development, and classroom resources. Without this, reforming the curriculum  risks widening existing inequalities in provision.

Read our full report

We believe listening to students and teachers should be central to curriculum reform. You can read the full report now:

The post What students and teachers in England want from a computing curriculum appeared first on Raspberry Pi Foundation.
UK Demanded Apple Add a Backdoor to iCloud

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2025/02/an-icloud-backdoor-would-make-our-phones-less-safe.html

Last month, the UK government demanded that Apple weaken the security of iCloud for users worldwide. On Friday, Apple took steps to comply for users in the United Kingdom. But the British law is written in a way that requires Apple to give its government access to anyone, anywhere in the world. If the government demands Apple weaken its security worldwide, it would increase everyone’s cyber-risk in an already dangerous world.

If you’re an iCloud user, you have the option of turning on something called “advanced data protection,” or ADP. In that mode, a majority of your data is end-to-end encrypted. This means that no one, not even anyone at Apple, can read that data. It’s a restriction enforced by mathematics—cryptography—and not policy. Even if someone successfully hacks iCloud, they can’t read ADP-protected data.

Using a controversial power in its 2016 Investigatory Powers Act, the UK government wants Apple to re-engineer iCloud to add a “backdoor” to ADP. This is so that if, sometime in the future, UK police wanted Apple to eavesdrop on a user, it could. Rather than add such a backdoor, Apple disabled ADP in the UK market.

Should the UK government persist in its demands, the ramifications will be profound in two ways. First, Apple can’t limit this capability to the UK government, or even only to governments whose politics it agrees with. If Apple is able to turn over users’ data in response to government demand, every other country will expect the same compliance. China, for example, will likely demand that Apple out dissidents. Apple, already dependent on China for both sales and manufacturing, won’t be able to refuse.

Second: Once the backdoor exists, others will attempt to surreptitiously use it. A technical means of access can’t be limited to only people with proper legal authority. Its very existence invites others to try. In 2004, hackers—we don’t know who—breached a backdoor access capability in a major Greek cellphone network to spy on users, including the prime minister of Greece and other elected officials. Just last year, China hacked U.S. telecoms and gained access to their systems that provide eavesdropping on cellphone users, possibly including the presidential campaigns of both Donald Trump and Kamala Harris. That operation resulted in the FBI and the Cybersecurity and Infrastructure Security Agency recommending that everyone use end-to-end encrypted messaging for their own security.

Apple isn’t the only company that offers end-to-end encryption. Google offers the feature as well. WhatsApp, iMessage, Signal, and Facebook Messenger offer the same level of security. There are other end-to-end encrypted cloud storage providers. Similar levels of security are available for phones and laptops. Once the UK forces Apple to break its security, actions against these other systems are sure to follow.

It seems unlikely that the UK is not coordinating its actions with the other “Five Eyes” countries of the United States, Canada, Australia, and New Zealand: the rich English-language-speaking spying club. Australia passed a similar law in 2018, giving it authority to demand that companies weaken their security features. As far as we know, it has never been used to force a company to re-engineer its security—but since the law allows for a gag order we might never know. The UK law has a gag order as well; we only know about the Apple action because a whistleblower leaked it to the Washington Post. For all we know, they may have demanded this of other companies as well. In the United States, the FBI has long advocated for the same powers. Having the UK make this demand now, when the world is distracted by the foreign-policy turmoil of the Trump administration, might be what it’s been waiting for.

The companies need to resist, and—more importantly—we need to demand they do. The UK government, like the Australians and the FBI in years past, argues that this type of access is necessary for law enforcement—that it is “going dark” and that the internet is a lawless place. We’ve heard this kind of talk since the 1990s, but its scant evidence doesn’t hold water. Decades of court cases with electronic evidence show again and again the police collect evidence through a variety of means, most of them—like traffic analysis or informants—having nothing to do with encrypted data. What police departments need are better computer investigative and forensics capabilities, not backdoors.

We can all help. If you’re an iCloud user, consider turning this feature on. The more of us who use it, the harder it is for Apple to turn it off for those who need it to stay out of jail. This also puts pressure on other companies to offer similar security. And it helps those who need it to survive, because enabling the feature couldn’t be used as a de facto admission of guilt. (This is a benefit of using WhatsApp over Signal. Since so many people in the world use WhatsApp, having it on your phone isn’t in itself suspicious.)

On the policy front, we have two choices. We can’t build security systems that work for some people and not others. We can either make our communications and devices as secure as possible against everyone who wants access, including foreign intelligence agencies and our own law enforcement, which protects everyone, including (unfortunately) criminals. Or we can weaken security—the criminals’ as well as everyone else’s.

It’s a question of security vs. security. Yes, we are all more secure if the police are able to investigate and solve crimes. But we are also more secure if our data and communications are safe from eavesdropping. A backdoor in Apple’s security is not just harmful on a personal level, it’s harmful to national security. We live in a world where everyone communicates electronically and stores their important data on a computer. These computers and phones are used by every national leader, member of a legislature, police officer, judge, CEO, journalist, dissident, political operative, and citizen. They need to be as secure as possible: from account takeovers, from ransomware, from foreign spying and manipulation. Remember that the FBI recommended that we all use backdoor-free end-to-end encryption for messaging just a few months ago.

Securing digital systems is hard. Defenders must defeat every attack, while eavesdroppers need one attack that works. Given how essential these devices are, we need to adopt a defense-dominant strategy. To do anything else makes us all less safe.

This essay originally appeared in Foreign Policy.

UK Is Ordering Apple to Break Its Own Encryption

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2025/02/uk-is-ordering-apple-to-break-its-own-encryption.html

The Washington Post is reporting that the UK government has served Apple with a “technical capability notice” as defined by the 2016 Investigatory Powers Act, requiring it to break the Advanced Data Protection encryption in iCloud for the benefit of law enforcement.

This is a big deal, and something we in the security community have worried was coming for a while now.

The law, known by critics as the Snoopers’ Charter, makes it a criminal offense to reveal that the government has even made such a demand. An Apple spokesman declined to comment.

Apple can appeal the U.K. capability notice to a secret technical panel, which would consider arguments about the expense of the requirement, and to a judge who would weigh whether the request was in proportion to the government’s needs. But the law does not permit Apple to delay complying during an appeal.

In March, when the company was on notice that such a requirement might be coming, it told Parliament: “There is no reason why the U.K. [government] should have the authority to decide for citizens of the world whether they can avail themselves of the proven security benefits that flow from end-to-end encryption.”

Apple is likely to turn the feature off for UK users rather than break it for everyone worldwide. Of course, UK users will be able to spoof their location. But this might not be enough. According to the law, Apple would not be able to offer the feature to anyone who is in the UK at any point: for example, a visitor from the US.

And what happens next? Australia has a law enabling it to ask for the same thing. Will it? Will even more countries follow?

This is madness.

The UK Bans Default Passwords

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/05/the-uk-bans-default-passwords.html

The UK is the first country to ban default passwords on IoT devices.

On Monday, the United Kingdom became the first country in the world to ban default guessable usernames and passwords from these IoT devices. Unique passwords installed by default are still permitted.

The Product Security and Telecommunications Infrastructure Act 2022 (PSTI) introduces new minimum-security standards for manufacturers, and demands that these companies are open with consumers about how long their products will receive security updates for.

The UK may be the first country, but as far as I know, California is the first jurisdiction. It banned default passwords in 2018, the law taking effect in 2020.

This sort of thing benefits all of us everywhere. IoT manufacturers aren’t making two devices, one for California and one for the rest of the US. And they’re not going to make one for the UK and another for the rest of Europe, either. They’ll remove the default passwords and sell those devices everywhere.

Another news article.

UK Threatens End-to-End Encryption

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2023/04/uk-threatens-end-to-end-encryption.html

In an open letter, seven secure messaging apps—including Signal and WhatsApp—point out that the UK’s Online Safety Bill could destroy end-to-end encryption:

As currently drafted, the Bill could break end-to-end encryption,opening the door to routine, general and indiscriminate surveillance of personal messages of friends, family members, employees, executives, journalists, human rights activists and even politicians themselves, which would fundamentally undermine everyone’s ability to communicate securely.

The Bill provides no explicit protection for encryption, and if implemented as written, could empower OFCOM to try to force the proactive scanning of private messages on end-to-end encrypted communication services—nullifying the purpose of end-to-end encryption as a result and compromising the privacy of all users.

In short, the Bill poses an unprecedented threat to the privacy, safety and security of every UK citizen and the people with whom they communicate around the world, while emboldening hostile governments who may seek to draft copy-cat laws.

Both Signal and WhatsApp have said that they will cease services in the UK rather than compromise the security of their users worldwide.

UK Runs Fake DDoS-for-Hire Sites

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2023/04/uk-runs-fake-ddos-for-hire-sites.html

Brian Krebs is reporting that the UK’s National Crime Agency is setting up fake DDoS-for-hire sites as part of a sting operation:

The NCA says all of its fake so-called “booter” or “stresser” sites -­ which have so far been accessed by several thousand people—have been created to look like they offer the tools and services that enable cyber criminals to execute these attacks.

“However, after users register, rather than being given access to cyber crime tools, their data is collated by investigators,” reads an NCA advisory on the program. “Users based in the UK will be contacted by the National Crime Agency or police and warned about engaging in cyber crime. Information relating to those based overseas is being passed to international law enforcement.”

The NCA declined to say how many phony booter sites it had set up, or for how long they have been running. The NCA says hiring or launching attacks designed to knock websites or users offline is punishable in the UK under the Computer Misuse Act 1990.

“Going forward, people who wish to use these services can’t be sure who is actually behind them, so why take the risk?” the NCA announcement continues.

AWS and the UK rules on operational resilience and outsourcing

Post Syndicated from Arvind Kannan original https://aws.amazon.com/blogs/security/aws-and-the-uk-rules-on-operational-resilience-and-outsourcing/

Financial institutions across the globe use Amazon Web Services (AWS) to transform the way they do business. Regulations continue to evolve in this space, and we’re working hard to help customers proactively respond to new rules and guidelines. In many cases, the AWS Cloud makes it simpler than ever before to assist customers with their compliance efforts with different regulations and frameworks around the world.

In the United Kingdom, the Financial Conduct Authority (FCA), the Bank of England and the Prudential Regulation Authority (PRA) issued policy statements and rules on operational resilience in March, 2021. The PRA also additionally issued a supervisory statement on outsourcing and third-party risk management. Broadly, these Statements apply to certain firms that are regulated by the UK Financial Regulators: this includes banks, building societies, credit unions, insurers, financial markets infrastructure providers, payment and e-money institutions, major investment firms, mixed activity holding companies, and UK branches of certain overseas firms. For other FCA-authorized financial services firms, the FCA has previously issued FG 16/5 Guidance for firms outsourcing to the ‘cloud’ and other third-party IT services.

These Statements are relevant to the use of cloud services. AWS strives to help support our customers with their compliance obligations and help them meet their regulator’s expectations. We offer our customers a wide range of services that can simplify and directly assist in complying with these Statements, which apply from March 2022.

What do these Statements from the UK Financial Regulators mean for AWS customers?

The Statements aim to ensure greater operational resilience for UK financial institutions and, in the case of the PRA’s papers on outsourcing, facilitate greater adoption of the cloud and other new technologies while also implementing the Guidelines on outsourcing arrangements from the European Banking Authority (EBA) and the relevant sections of the EBA Guidelines on ICT and security risk management. (See the AWS approach to these EBA guidelines in this blog post).

For AWS and our customers, the key takeaway is that these Statements provide a regulatory framework for cloud usage in a resilient manner. The PRA’s outsourcing paper, in particular, sets out conditions that can help give PRA-regulated firms assurance that they can deploy to the cloud in a safe and resilient manner, including for material, regulated workloads. When they consider or use third-party services (such as AWS), many UK financial institutions already follow due diligence, risk management, and regulatory notification processes that are similar to the processes identified in these Statements, the EBA Outsourcing Guidelines, and FG 16/5. UK financial institutions can use a variety of AWS security and compliance services to help them meet requirements on security, resilience, and assurance.

Risk-based approach

The Statements reference the principle of proportionality throughout. In the case of the outsourcing requirements, this includes a focus on material outsourcing arrangements and incorporating a risk-based approach that expects regulated entities to identify, assess, and mitigate the risks associated with outsourcing arrangements. The recognition of a shared responsibility model, referenced by the PRA and the recognition in FCA Guidance FG 16/5 that firms need to be clear about where responsibility lies between themselves and their service providers, is consistent with the long-standing AWS shared responsibility model. The proportionality and risk-based approach applies throughout the Statements, including the areas such as risk assessment, contractual and audit requirements, data location and transfer, operational resilience, and security implementation:

  • Risk assessment – The Statements emphasize the need for UK financial institutions to assess the potential impact of outsourcing arrangements on their operational risk. The AWS shared responsibility model helps customers formulate their risk assessment approach, because it illustrates how their security and management responsibilities change depending on the services from AWS they use. For example, AWS operates some controls on behalf of customers, such as data center security, while customers operate other controls, such as event logging. In practice, AWS helps customers assess and improve their risk profile relative to traditional, on-premises environments.
     
  • Contractual and audit requirements – The PRA supervisory statement on outsourcing and third-party risk management, the EBA Outsourcing Guidelines, and the FCA guidance FG 16/5 lay out requirements for the written agreement between a UK financial institution and its service provider, including access and audit rights. For UK financial institutions that are running regulated workloads on AWS, please contact your AWS account team to address these contractual requirements. We also help institutions that require contractual audit rights to comply with these requirements through the AWS Security & Audit Series, which facilitates customer audits. To align with regulatory requirements and expectations, our audit program incorporates feedback that we’ve received from EU and UK financial supervisory authorities. UK financial services customers interested in learning more about the audit engagements offered by AWS can reach out to their AWS account teams.
     
  • Data location and transfer – The UK Financial Regulators do not place restrictions on where a UK financial institution can store and process its data, but rather state that UK financial institutions should adopt a risk-based approach to data location. AWS continually monitors the evolving regulatory and legislative landscape around data privacy to identify changes and determine what tools our customers might need to help meet their compliance needs. Refer to our Data Protection page for our commitments, including commitments on data access and data storage.
     
  • Operational resilience – Resiliency is a shared responsibility between AWS and the customer. It is important that customers understand how disaster recovery and availability, as part of resiliency, operate under this shared model. AWS is responsible for resiliency of the infrastructure that runs all of the services offered in the AWS Cloud. This infrastructure comprises the hardware, software, networking, and facilities that run AWS Cloud services. AWS uses commercially reasonable efforts to make these AWS Cloud services available, ensuring that service availability meets or exceeds the AWS Service Level Agreements (SLAs).

    The customer’s responsibility will be determined by the AWS Cloud services that they select. This determines the amount of configuration work they must perform as part of their resiliency responsibilities. For example, a service such as Amazon Elastic Compute Cloud (Amazon EC2) requires the customer to perform all of the necessary resiliency configuration and management tasks. Customers that deploy Amazon EC2 instances are responsible for deploying EC2 instances across multiple locations (such as AWS Availability Zones), implementing self-healing by using services like AWS Auto Scaling, as well as using resilient workload architecture best practices for applications that are installed on the instances.

    For managed services, such as Amazon Simple Storage Service (Amazon S3) and Amazon DynamoDB, AWS operates the infrastructure layer, the operating system, and platforms, whereas customers access the endpoints to store and retrieve data. Customers are responsible for managing resiliency of their data, including backup, versioning, and replication strategies. For more details about our approach to operational resilience in financial services, refer to this whitepaper.

  • Security implementation – The Statements set expectations on data security, including data classification and data security, and require UK financial institutions to consider, implement, and monitor various security measures. Using AWS can help customers meet these requirements in a scalable and cost-effective way, while helping improve their security posture. Customers can use AWS Config or AWS Security Hub to simplify auditing, security analysis, change management, and operational troubleshooting.

    As part of their cybersecurity measures, customers can activate Amazon GuardDuty, which provides intelligent threat detection and continuous monitoring, to generate detailed and actionable security alerts. Amazon Macie uses machine learning and pattern matching to help customers classify their sensitive and business-critical data in AWS. Amazon Inspector automatically assesses a customer’s AWS resources for vulnerabilities or deviations from best practices and then produces a detailed list of security findings prioritized by level of severity.

    Customers can also enhance their security by using AWS Key Management Service (AWS KMS) (creation and control of encryption keys), AWS Shield (DDoS protection), and AWS WAF (helps protect web applications or APIs against common web exploits). These are just a few of the many services and features we offer that are designed to provide strong availability and security for our customers.

As reflected in these Statements, it’s important to take a balanced approach when evaluating responsibilities in cloud implementation. AWS is responsible for the security of the AWS infrastructure, and for all of our data centers, we assess and manage environmental risks, employ extensive physical and personnel security controls, and guard against outages through our resiliency and testing procedures. In addition, independent third-party auditors evaluate the AWS infrastructure against more than 2,600 standards and requirements throughout the year.

Conclusion

We encourage customers to learn about how these Statements apply to their organization. Our teams of security, compliance, and legal experts continue to work with our UK financial services customers, both large and small, to support their journey to the AWS Cloud. AWS is closely following how the UK regulatory authorities apply the Statements and will provide further updates as needed. If you have any questions about compliance with these Statements and their application to your use of AWS, reach out to your account representative or request to be contacted.

 
Want more AWS Security news? Follow us on Twitter.

Arvind Kannan

Arvind Kannan

Arvind is a Principal Compliance Specialist at Amazon Web Services based in London, United Kingdom. He spends his days working with financial services customers in the UK and across EMEA, helping them address questions around governance, risk and compliance. He has a strong focus on compliance and helping customers navigate the regulatory requirements and understand supervisory expectations.

Brexit Deal Mandates Old Insecure Crypto Algorithms

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2020/12/brexit-deal-mandates-old-insecure-crypto-algorithms.html

In what is surely an unthinking cut-and-paste issue, page 921 of the Brexit deal mandates the use of SHA-1 and 1024-bit RSA:

The open standard s/MIME as extension to de facto e-mail standard SMTP will be deployed to encrypt messages containing DNA profile information. The protocol s/MIME (V3) allows signed receipts, security labels, and secure mailing lists… The underlying certificate used by s/MIME mechanism has to be in compliance with X.509 standard…. The processing rules for s/MIME encryption operations… are as follows:

  1. the sequence of the operations is: first encryption and then signing,
  2. the encryption algorithm AES (Advanced Encryption Standard) with 256 bit key length and RSA with 1,024 bit key length shall be applied for symmetric and asymmetric encryption respectively,
  3. the hash algorithm SHA-1 shall be applied.
  4. s/MIME functionality is built into the vast majority of modern e-mail software packages including Outlook, Mozilla Mail as well as Netscape Communicator 4.x and inter-operates among all major e-mail software packages.

And s/MIME? Bleah.

Configuring AWS VPN for UK public sector use

Post Syndicated from Charlie Llewellyn original https://aws.amazon.com/blogs/security/configuring-aws-vpn-for-uk-public-sector-use/

In this post, we explain the United Kingdom (UK) National Cyber Security Centre (NCSC)’s guidance on VPN profiles configuration, and how the configuration parameters for the AWS Virtual Private Network (AWS VPN) align with the NCSC guidance. At the end of the post, there are links to code to deploy the AWS VPN in line with those parameters.

Many public sector organizations in the UK need to connect their existing on-premises facilities, data centers, or offices to the Amazon Web Services (AWS) cloud so they can take advantage of the broad set of services AWS provides to help them deliver against their mission.

This can be achieved using the AWS VPN service. However some customers find it difficult to know the exact configuration parameters that they should choose when establishing the VPN connection in-line with guidance for the UK public sector.

AWS VPN services enable organizations to establish secure connections between their on-premises networks, remote offices, and client devices and the AWS global network. AWS VPN comprises two services: AWS Site-to-Site VPN and AWS Client VPN. Together, they deliver a highly available, fully managed, elastic cloud VPN solution to protect your network traffic.

For the purposes of this post, we focus on the Site-to-Site VPN configuration, not Client VPN because the NCSC guidance we’re discussing is specifically related to site-to-site VPNs. This post covers two areas:

  • An overview of the current guidance for VPN configurations for the public sector.
  • Recommendations on how to configure AWS VPN to meet or exceed the current guidance.

VPN guidance for UK public sector organizations

The starting point for security guidance for the UK public sector is often the NCSC. The role of the NCSC includes:

  • Protecting government systems and information.
  • Planning for and responding to cyber incidents.
  • Working with providers of critical national infrastructure to improve the protection and computer security of such infrastructure against cyber-borne threats.

Specifically, for guidance on the configuration of VPNs for the UK public sector to support data at OFFICIAL, the NCSC has created detailed guidance on the technical configurations to support two different profiles: PRIME and Foundation. These two profiles provide different technical implementations to support different equipment and are both suitable for use with OFFCICIAL data. Beyond these technical differences, NCSC also documents that Foundation is expected to provide suitable protection for OFFICIAL information until at least December 31, 2023, while PRIME has no review date specified at the time of writing.

This guidance is available in Using IPsec to protect data.

Let’s start by debunking a few myths.

Myth 1: I have to adhere exactly to the NCSC technical configuration or I cannot use a VPN for OFFICIAL data

It’s a common misconception that a public sector organization must adhere exactly to the configuration of either PRIME or Foundation in order to use a VPN for OFFICIAL data, even if other configuration options available—such as a longer key length—offer a higher security baseline.

Note that the NCSC isn’t mandating the use of the configuration in their guidance. They’re offering a configuration that provides a useful baseline, but you must assess your use of the NCSC guidance in context of the risks. To help with these risk-based decisions, the NCSC has developed a series of guidance documents to help organizations make risk-based decisions. A common consideration that might require deviating from the guidance would be supporting interoperability with legacy systems where the suggested algorithms aren’t supported. In this case, a risk-based decision should be made—including accounting for other factors such as cost.

It’s also worth noting that the NCSC creates guidance designed to be useful to as many organizations as possible. The NCSC balances adopting the latest possible configurations with backwards compatibility and vendor support. For example, the NCSC suggests AES-128 where—in theory—AES-256 could also be a good choice. Organizations need to be aware that if they choose to adopt devices that support only AES-256 and later need to connect in devices capable of only AES-128, there could be significant investment to replace the legacy devices with ones that support AES-256. However, AWS provides both AES-128 and AES-256, so if the remote device supports it, AWS would recommend opting for AES-256.

The NCSC also tries to develop advice that has some longevity. For example, the guidance suggesting use of AES-128 was created in 2012 with a view to providing solid guidance over a number of years. This means customers can choose different configuration parameters that offer increased levels of security if both sides of the VPN can support it.

It’s possible for a customer to choose options that might lower the security of the connection, provided that risks are identified and appropriately managed by the customers assurance team. This might be needed to support interoperability between existing systems where the cost of an upgrade outweighs the risk.

Myth 2: Foundation has been deprecated and I must use PRIME

Another common misconception is that Foundation has been deprecated in favor of PRIME. This is not the case. The NCSC has stated that Foundation is expected to provide suitable protection for OFFICIAL information until at least December 31, 2023. The security provided by both solutions provides commensurate security for accessing data classified as OFFICIAL. One of the main differences between PRIME and Foundation is the choice of signature algorithm: RSA or ECDSA. This difference can be helpful in enabling an organization to choose which profile to adopt. For example, if the organization already has a private key infrastructure (PKI), then the decision regarding which signature algorithm to use is based on what existing systems support.

Myth 3: I can’t use Foundation for accessing OFFICIAL SENSITIVE data

A final point that often causes confusion is the classifying of data at OFFICIAL SENSITIVE because it isn’t a classification, but a handling caveat. The data would be classified as OFFICIAL and marked as OFFICIAL SENSITIVE, meaning that systems handling the data need risk-appropriate security measures. A system that can handle OFFICIAL data might be appropriate to handle sensitive information. Hence Foundation could be suitable for accessing OFFICIAL SENSITIVE data, depending on the risks identified.

Deep-dive into the technical specifications

Now that you know a little more about how the guidance should be viewed, let’s look more closely at the technical configurations for each VPN profile.

The following table shows the configuration parameters suggested by the NCSC VPN guidance discussed previously.

Technical detail Foundation PRIME
IKEv* – Encryption IKEv1 – AES with 128-bit keys in CBC mode (RFC3602) IKEv2 – AES-128 in GCM-128 (and optionally CBC)
IKEv2 – Pseudo-random function HMAC-SHA256 HMAC-SHA256
IKEv2 – Diffie-Hellman group Group 14 (2048-bit MODP group) (RFC3526) 256 bit random ECP (RFC5903) Group 19
IKEv2 – Authentication X.509 certificates with RSA signatures (2048 bits) and SHA-256 (RFC4945 and RFC4055) X.509 certificates with ECDSA-256 with SHA256 on P-256 curve
ESP – Encryption AES with 128-bit keys in CBC mode (RFC3602)
SHA-256 (RFC4868)
AES-128 in GCM-128
SHA-256 (RFC4868)

Recommended AWS VPN configuration for public sector

Bearing in mind these policies, and remembering that the configuration is only guidance, you must make a risk-based decision. AWS recommends the following configuration as a starting point for the configuration of the AWS VPN.

Technical detail AWS configuration Adherence
IKEv* – Encryption IKEv2 – AES-256-GCM Suitable for Foundation and PRIME
IKEv2 – Pseudo-random function HMAC-SHA256 Meets Foundation and PRIME
IKEv2 – Diffie-Hellman group Group 19 Suitable for Foundation and matches PRIME
IKEv2 – Authentication RSA 2048 SHA2-512 Suitable for Foundation
ESP – Encryption AES-256-GCM Suitable for PRIME and Foundation

In the table above, we use the term suitable for where the protocol doesn’t match the guidance exactly but the AWS configuration options provide equivalent or stronger security—for example, by using a longer key length.

With the configuration defined above, the AWS VPN service is suitable for use under the Foundation profile in all areas. It can also be made suitable for PRIME in all areas apart from IKEv2 encryption. The use of RSA or ECDSA is the main difference between the AWS VPN and PRIME configurations. This makes the current AWS VPN solution closer to Foundation than PRIME.

When considering which options are available to you, the starting point should be the capabilities of your current—and possible future—VPN devices. Based on its capabilities, you can use the NCSC guidance and preceding tables to choose the protocols that match or are suitable for the NCSC guidance.

Summary

To review:

  • The NCSC provides guidance for the VPN configuration, not a mandate.
  • An organization is free to decide not to use the guidance, but should consider risks when they make that decision.
  • The AWS VPN meets or is suitable for the configuration options for Foundation.

After reviewing the details contained in this blog, UK public sector organizations should have the confidence to use the AWS VPN service with systems running at OFFICIAL.

If you’re interested in deploying the AWS VPN configuration described in this post, you can download instructions and AWS CloudFormation templates to configure the AWS VPN service. The AWS VPN configuration can be deployed to either connect directly to a single Amazon Virtual Private Cloud (Amazon VPC) using a virtual private gateway, or to an AWS Transit Gateway to enable its use by multiple VPCs.

If you’re interested in configuring your AWS VPN tunnel options manually, you can follow Modifying Site-to-Site VPN tunnel options.

If you have feedback about this post, submit comments in the Comments section below.

Want more AWS Security how-to content, news, and feature announcements? Follow us on Twitter.

Author

Charlie Llewellyn

Charlie is a Solutions Architect working in the Public Sector team with Amazon Web Services. He specializes in data analytics and enjoys helping customers use data to make better decisions. In his spare time he avidly enjoys mountain biking and cooking.

Author

Muhammad Khas

Muhammad Khas is a Solutions Architect working in the Public Sector team at Amazon Web Services. He enjoys supporting customers in using artificial intelligence and machine learning to enhance their decision making. Outside of work, Muhammad enjoys swimming, and horse riding.