Post Syndicated from Explosm.net original https://explosm.net/comics/government-guy
New Cyanide and Happiness Comic
Post Syndicated from Explosm.net original https://explosm.net/comics/government-guy
New Cyanide and Happiness Comic
Post Syndicated from The History Guy: History Deserves to Be Remembered original https://www.youtube.com/watch?v=6JDu17Va-GQ
Post Syndicated from turnoff.us original http://turnoff.us/geek/too-many-indexes/
Post Syndicated from Meg Wang original https://www.raspberrypi.org/blog/hello-world-23-global-computing-education-ideas/
How is computing taught around the globe? Our brand-new, free issue of Hello World, out today, paints a picture for you. It features stories from over 20 countries, where educators, researchers, and volunteers share their work and their personal challenges and joys in bringing computing education to their part of the world.
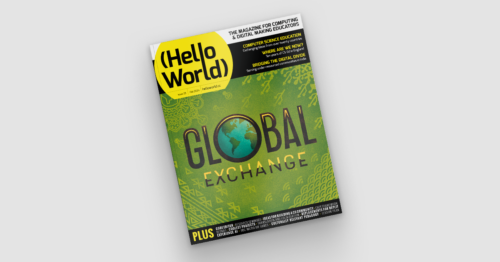
In Hello World issue 23, you’ll hear about countries where computing is an official school subject and how it was set up that way, and you’ll hear about countries that are newer to computing education and working to fast-track their students’ learning.
And there is lots more for you to discover in issue 23.
Sue Sentance, director of the Raspberry Pi Computing Education Research Centre at the University of Cambridge, says in her article:
“Our own experience of implementing computing education in England since 2014 has shown the importance of teachers supporting each other, and how various networks … are instrumental in bringing computing teachers together to share knowledge and experiences. With so many countries introducing computing education, and teachers around the globe facing similar challenges, maybe we need to extend this to a global teacher network, where teachers and policymakers can share good practice and learn from each other. “
We aim for Hello World magazine to be one of the places where this sharing, exchange, and learning can take place. Subscribe for free to never miss an issue, and find out how you can write for the magazine.
Research highlights the importance of computing education to young people’s futures, whether or not they pursue a degree or career in the area. From teaching computing in schools where the electricity cuts out, to incorporating artificial intelligence into curricula in different countries, and to teaming up with local governments when there isn’t a national computing curriculum, educators are doing wonderful things around the globe to make sure the young people they support have the opportunity to learn. Read their stories today.
Also in issue 23:
And much, much more.
Send us a message or tag us on social media to let us know which articles have made you think, and most importantly, which will help you with your teaching. And to hear monthly news about Hello World and the whole Raspberry Pi Foundation, sign up to the Hello World newsletter.
The post Hello World #23 out now: Global exchange of computing education ideas appeared first on Raspberry Pi Foundation.
Post Syndicated from Petra Arts http://blog.cloudflare.com/author/petra/ original https://blog.cloudflare.com/digital-services-act
February 17th, 2024 marked the entry into force of a landmark piece of European Union (EU) legislation, affecting European users who create and disseminate online content as well as tech companies who act as “intermediaries” on the Internet. I am talking of course about the EU Digital Services Act, or DSA for short. The DSA was first proposed in December 2020, and is meant to update a 20-year-old law called the EU e-commerce Directive, which provides important safeguards and legal certainty for all businesses operating online. The principles of that legal framework, most notably the introduction of EU-wide rules on intermediary liability, are still of major importance today. The DSA is a landmark piece of European legislation because it also sets out, for the first time, enhanced regulatory requirements for (large) digital platforms, thus affecting the entire Internet ecosystem.
At Cloudflare, we are supportive of the longstanding legal frameworks both in Europe and other parts of the world that protect Internet companies from liability for the content that is uploaded or sent through their networks by their users, subscribers or customers. These frameworks are indispensable for the growth of online services, and have been essential in the growth of online applications, marketplaces and social networks.
The EU Digital Services Act consists of two main parts: First, the DSA maintains the strong liability protections for intermediary services that have existed in Europe for over 20 years, and modernizes them, including by giving explicit recognition of supporting Internet services. Services which perform important roles in the functioning of the Internet, such as CDNs, reverse proxies and technical services at the DNS level were not explicitly mentioned in the EU e-commerce Directive at the time. The DSA, in recital 28, recognises that those services, along with many others, are part of the fundamental fabric of the Internet and deserve protection against liability for any illegal or infringing content. This marks an important clarification milestone in EU law.
Secondly, the DSA establishes varying degrees of due diligence and transparency obligations for intermediary services that offer services in the EU. The DSA follows a ‘staggered’ or ‘cumulative’ approach to those obligations and the different services it applies to. This ranges from a number of detailed obligations for the largest platforms (so-called “Very Large Online Platforms” or VLOPs, such as the Apple App Store, Facebook, TikTok, and YouTube), down to less extensive but still impactful rules for smaller platforms, hosting services and Internet intermediaries. What is really important to note with regard to the different service providers that are impacted is that the DSA clearly distinguishes between (technical) intermediary services, “mere” hosting services, and “online platforms”, with the latter category having a number of additional obligations under the new law. Online platform services are considered as hosting services which store information at the request of the recipients of the service, with the important additional role of also disseminating that information to the public.
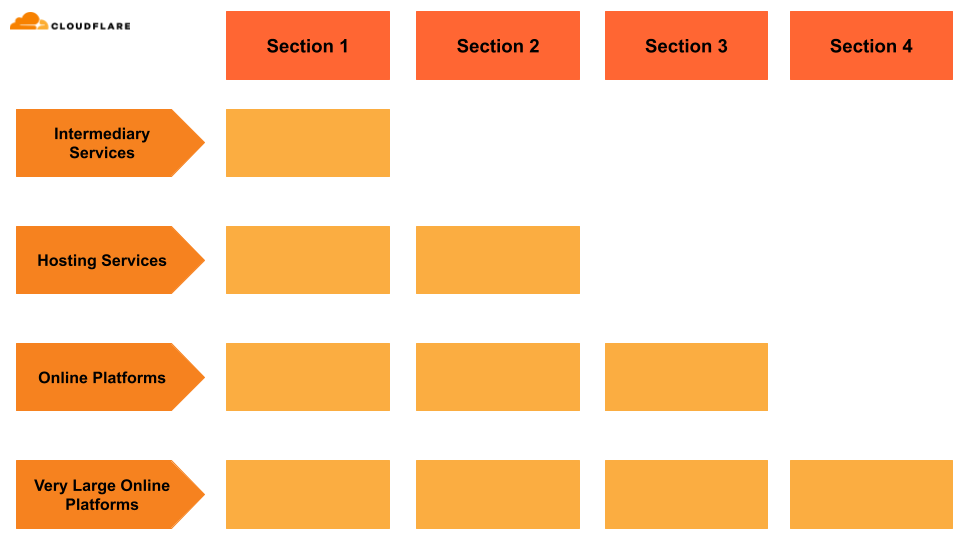
This proportionate approach is in line with Cloudflare’s view of the Internet stack and the idea that infrastructure services are distinct from social media and search services that are designed to curate and recommend Internet content. This principle of a targeted, proportionate response to the matter is also embedded in the DSA itself. Recital 27 states that “(…) any requests or orders for [such] involvement should, as a general rule, be directed to the specific provider that has the technical and operational ability to act against specific items of illegal content, so as to prevent and minimise (sic) any possible negative effects on the availability and accessibility of information that is not illegal content”. This is an important provision, as principles of proportionality, freedom of speech, and access to information should be safeguarded at all times when it relates to online content.
As a provider of intermediary services, Cloudflare has engaged with European policymakers on the topic of intermediary liability for a number of years. From the start of the legislative process on the proposed DSA in 2020 we have contributed extensively to public consultations, and have shared our views on the proposed DSA with lawmakers in Brussels.
In many ways, the final version of the law reflects our existing practices. We have long taken the position, for example, that our intermediary services should have different rules than our hosting services, as is anticipated under the DSA. We have taken a few additional measures to ensure compliance with DSA requirements. For instance, we’ve announced a new legal representative in the EU and point of contact for the purposes of the DSA.
Cloudflare has strongly believed in transparency reporting for a long time, and we have issued transparency reports twice a year since 2013. We recognize that the DSA includes some new requirements around transparency reporting, some of which match with our current reports and processes, and others that do not. We will be revising our transparency reporting, to reflect the DSA’s requirements, beyond our existing documentation. We have also taken steps to confirm that our limited hosting services comply with DSA requirements.
The EU Digital Services Act, because of its enhanced regulatory requirements for (large) digital platforms, represents a significant change to the Internet ecosystem. Cloudflare feels nonetheless well-prepared to address the different requirements that came into force on February 17, 2024, and we look forward to having positive and constructive conversations with relevant European regulators as they start to work on the enforcement of the new law.
Post Syndicated from Eric Smith original https://www.servethehome.com/how-to-start-stop-and-list-proxmox-ve-virtual-machines-via-the-cli/
We have a quick guide if you need to use the CLI shell in Proxmox VE to list, start, stop, restart, shutdown, suspend, or resume VMs
The post How to Start Stop and List Proxmox VE Virtual Machines via the CLI appeared first on ServeTheHome.
Post Syndicated from xkcd.com original https://xkcd.com/2896/
Post Syndicated from corbet original https://lwn.net/Articles/962668/
The 6.8-rc5 kernel prepatch is out for
testing. “Absolutely nothing stands out here, although I do wish
“
things should have calmed down a bit more at this point in the release
process.
Post Syndicated from Explosm.net original https://explosm.net/comics/your-wife
New Cyanide and Happiness Comic
Post Syndicated from Oglaf! -- Comics. Often dirty. original https://www.oglaf.com/educational-content/


Post Syndicated from Eric Smith original https://www.servethehome.com/qnap-tr-004-usb-raid-enclosure-review-seagate-wd/
In our QNAP TR-004 review, we see how this USB RAID enclosure can quickly expand the storage of a NAS or PC with several RAID options
The post QNAP TR-004 USB RAID Enclosure Review appeared first on ServeTheHome.
Post Syndicated from Techmoan original https://www.youtube.com/watch?v=vm6FnjL3STw
Post Syndicated from Йовко Ламбрев original https://www.toest.bg/sedmitsata-12-17-fevruari/

Точно в деня на любовта и виното цялото ръководство на Софийската районна прокуратура подаде оставка. Това, разбира се, е отзвук от убийството на Мартин Божанов, наричан Нотариуса, но онова, което предизвика оставките, беше интервюто на Слави Ангелов с Анастасиос Дикос, представител на голям инвеститор у нас. Той разказа от първо лице за натиска, на който е бил подложен бизнесът му, и за нечистоплътните взаимовръзки между брокерите на влияние, данъчни служители и ръководителката на Районната прокуратура в столицата.
Дилърите на правосъдие, които със съдействието на прокурори, съдии и служители на ДАНС, МВР и НАП са упражнявали своето разбиране за „върховенство на правото“, са тема и на анализа на Емилия Милчева тази седмица „Кой се страхува от трупа на Нотариуса“. И големият въпрос: кой е в състояние да разплете кълбото от зависимости, когато дори временно изпълняващият функциите главен прокурор трудно може да бъде отделен от своето минало?
 Емилия Милчева
Иначе, след убийството на Мартин Божанов – Нотариуса на повърхността изплуват все повече детайли за нерегламентираните зависимости между ключови представители на институциите, жълто-кафяви „медии“ и групите за натиск. Добрата новина е, че значителна част от схемата е осветлена. Лошата е, че надделяват ступорът и снишаването, а досегашните оставки изобщо не са достатъчни. Много добро обобщение на най-важното до този момент прави Борис Митов за „Свободна Европа“.
Друг задължителен журналистически материал, който е добре да не пропускате тази седмица, е на Йоан Запрянов в „Капитал“. Особено ако се вълнувате от темата за дигиталните услуги, електронната идентификация и машинното гласуване. Статията разкрива интересни взаимоотношения от кухнята на Министерството на електронното управление. Възможно ли е структурата, призвана да управлява тези процеси, да ги саботира и обезсмисля? И то чрез настоящия си ръководител – министър Александър Йоловски.
В петък пред Министерския съвет в София и няколко града в страната се проведоха протести под надслов „Вън мафията от здравеопазването“. Повод за тях станаха журналистическите разкрития на Валя Ахчиева по случая със смъртта на 15-годишната Даная Кулева в „Пирогов“ миналото лято. Разкрития, свидетелстващи за системни проблеми и безчовечност, които нямат място в системата на което и да е здравеопазване. Вече е образувано досъдебно производство от Софийската градска прокуратура.
А в нашата поредица „Разговори за здравеопазването“, която също има за цел да дискутира проблемите в сектора и техните възможни решения, Надежда Цекулова този път ни среща с д-р Славяна Галева, акушер-гинеколог, преподавател и началник на отделението по фетална медицина към болница „Шейново“. Качеството на родилната помощ у нас страда от липса на съвременно разбиране, на достатъчно ясни правила, основани на наука, и на достатъчно строг контрол. Привидно всички сме съгласни с това, но вече десетилетия тази липса си стои. Разговор за причините, които са повече, отколкото предполагаме…
Надежда Цекулова
В петък в руска затворническа колония, на 47-годишна възраст, внезапно е починал Алексей Навални. Поне според официалната формулировка. Но важно е да припомним, че всъщност той е на мушката на режима на Путин от много време насам. През 2020-та оцеля след опит за отравяне с новичок, а през 2021-ва беше хвърлен в затвора по политически причини. Той бе един от най-активните и влиятелни критици на Путин. Само преди няколко дни призова за протести в цяла Русия по време на предстоящите президентски избори. Може да си припомните документалния филм „Навални“, продуциран от HBO Max и CNN Films.
Аексей Навальный отвечает на вопрос, что делать, если его убьют
Отрывок из фильма «Навальный» Дэниела Рора, 2022 год pic.twitter.com/vseatGh4DD
— Дождь (@tvrain) February 16, 2024
За съжаление, съвсем скоро ще се навършат две години от началото на войната в Украйна. В тази връзка публикуваме есе на украинския поет и преводач Олег Коцарев, което той написа специално за читателите на „Тоест“ (преводът е на Нева Мичева). „На езика на войната“ ни разхожда из смисъла на думите, с които тя, войната, все ни застига. Важен е не само лексикалният пласт, но и емоционалният, човешкият контекст, в който езиковата реалност може да има различни нюанси и отражения.
Олег Коцарев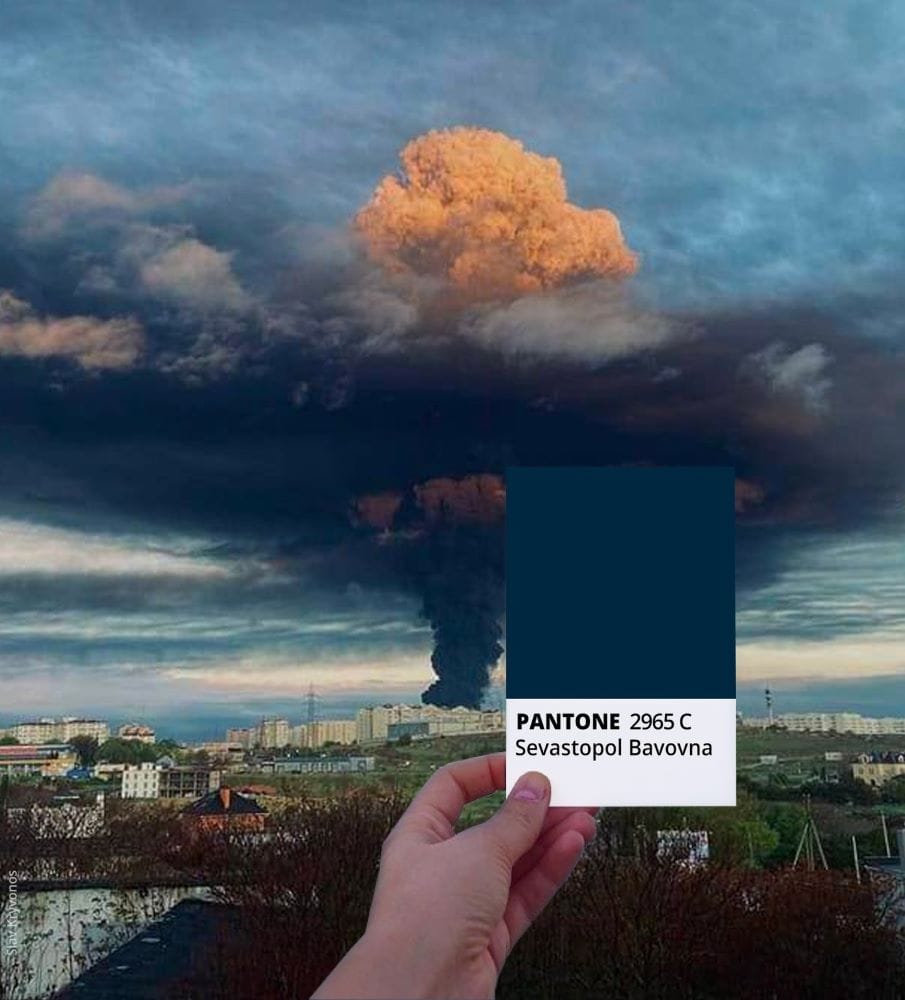
И докато сме още на езикова вълна – един материал по тема, която винаги е била ключова за „Тоест“. В него разказваме как функционира книжната екосистема и кои са важните герои в нея, редом с авторите и преводачите. Прочетете повече за проекта „Ускорител за балкански преводи“ на фондация „Следваща страница“.
Тоест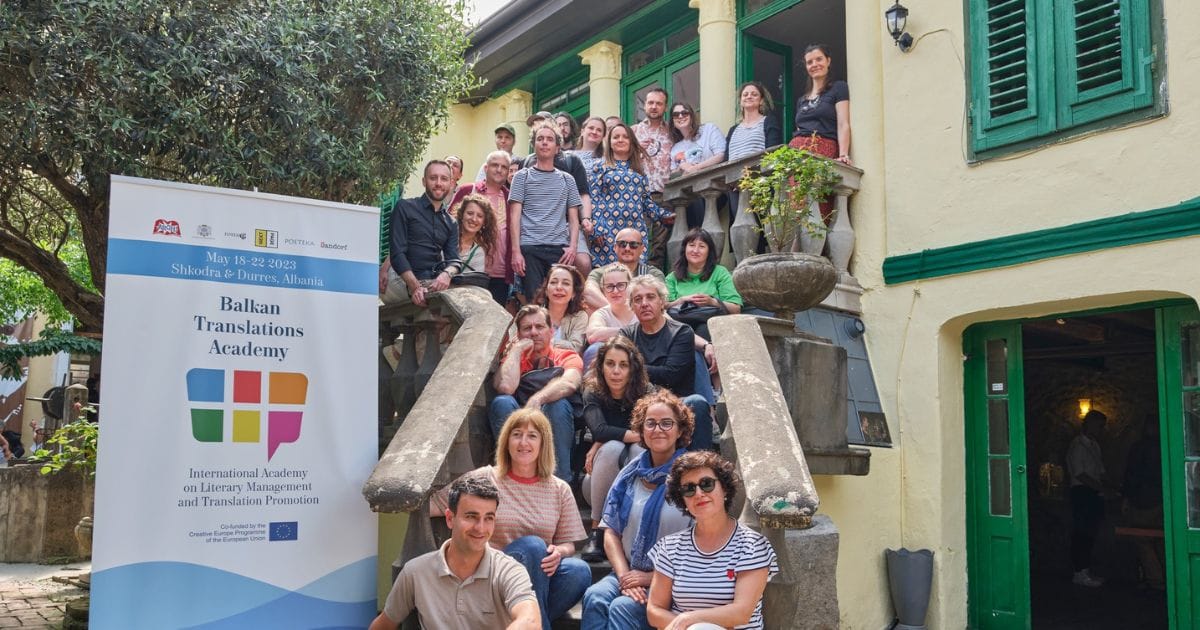
Емине Садкъ продължава поредицата си за гастарбайтерската песен, с която ни връща към 90-те години на ХХ век, когато децата на турските гастарбайтери в Германия градят идентичността си през субкултурни общности и с музиката си дават отпор на неонацистките движения. Ако и вие сте останали заинтригувани от първия ѝ текст, не пропускайте тази седмица продължението с провокативното заглавие „Майната ви, тук сме!“.
Емине Садкъ
И една тема, която само на пръв поглед изглежда незначителна, доколкото е свързана с не особено популярно вечерно шоу по Българската национална телевизия. Светла Енчева обръща внимание на много важни детайли, които бяха пометени от Facebook бурята на възпаленото обществено възмущение. Прочетете повече в нейния коментар, озаглавен „Андреа и банда банда хейтъри“.
Светла Енчева
Нека тази февруарска седмица да завършим изненадващо с ново начало – на една дълга северна поредица, която ще следим в продължение на няколко месеца и чийто автор е Светла Стоянова. Първият ѝ текст ни отвежда до Гренландия – до фиорда Кангиа, където всичко ухае на лед с история. А наоколо нещо съска, припуква и понякога дори трещи.
Светла Стоянова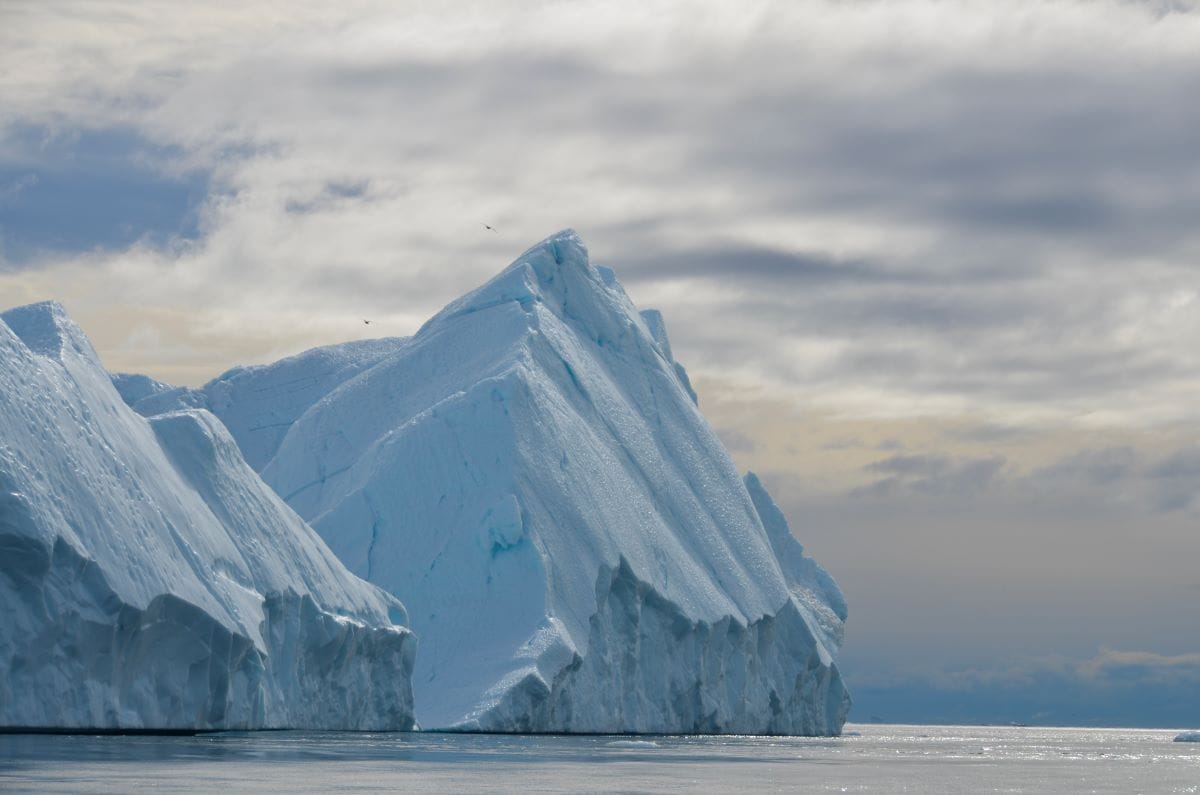
Приятно четене!
Post Syndicated from Explosm.net original https://explosm.net/comics/shooter-2
New Cyanide and Happiness Comic
Post Syndicated from Curious Droid original https://www.youtube.com/watch?v=-3JxCBSVZ9U
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/02/friday-squid-blogging-vegan-squid-ink-pasta.html
It uses black beans for color and seaweed for flavor.
As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.
Read my blog posting guidelines here.
Post Syndicated from jzb original https://lwn.net/Articles/962553/
The openSUSE News blog looks at the roadmap for Agama (a new installer from the YaST development team) with releases planned for April and July:
The milestone in April is set to revolutionize Agama’s architecture. It will be moving away from its reliance on Cockpit toward a more autonomous framework that is coupled with a refined user interface that aims to streamline storage configurations.
The aim of the second milestone is to improve Agama’s flexibility and capabilities for unattended installations, which seeks to position Agama as a formidable alternative to AutoYaST.
The Agama page explains why YaST is due for replacement.
Post Syndicated from Spencer McIntyre original https://blog.rapid7.com/2024/02/16/metasploit-weekly-wrap-up-02-16-2024/
It has been almost a year since Metasploit released the new fetch payloads and since then, 43 of the 79 exploit modules have had support for fetch payloads. The original payloads supported transferring the second stage over HTTP, HTTPS and FTP. This week, Metasploit has expanded that protocol support to include SMB, allowing payloads to be run using rundll32 which has the added benefit of capturing the NetNTLM hashes of the requestor.
This also streamlines the workflow the user would have previously used by first starting the exploit/windows/smb/smb_delivery module, and then copying the command into another exploit. Now the user can simply select one of the SMB-enabled fetch payloads and Metasploit will manage the service and generate the command.
As an added benefit, since #18680 merged into Metasploit, multiple SMB services can be run simultaneously. This means that multiple SMB-enabled fetch payloads can have their own independent handlers running at the same time.
Author: Spencer McIntyre
Type: Encoder
Pull request: #18807 contributed by zeroSteiner
Description: This adds a new encoder module that leverages base64 encoding to escape bad characters in ARCH_CMD payloads for the Linux and UNIX platforms.
Authors: Spencer McIntyre, bwatters-r7, and sf [email protected]
Type: Payload (Adapter)
Pull request: #18664 contributed by zeroSteiner
Description: This adds an SMB fetch-payload service and a new payload to use it. The payload invokes rundll32 but handles everything for the user automatically.
This adapter adds the following payloads:
cmd/windows/smb/x64/custom/bind_ipv6_tcpcmd/windows/smb/x64/custom/bind_ipv6_tcp_uuidcmd/windows/smb/x64/custom/bind_named_pipecmd/windows/smb/x64/custom/bind_tcpcmd/windows/smb/x64/custom/bind_tcp_rc4cmd/windows/smb/x64/custom/bind_tcp_uuidcmd/windows/smb/x64/custom/reverse_httpcmd/windows/smb/x64/custom/reverse_httpscmd/windows/smb/x64/custom/reverse_named_pipecmd/windows/smb/x64/custom/reverse_tcpcmd/windows/smb/x64/custom/reverse_tcp_rc4cmd/windows/smb/x64/custom/reverse_tcp_uuidcmd/windows/smb/x64/custom/reverse_winhttpcmd/windows/smb/x64/custom/reverse_winhttpscmd/windows/smb/x64/encrypted_shell/reverse_tcpcmd/windows/smb/x64/encrypted_shell_reverse_tcpcmd/windows/smb/x64/execcmd/windows/smb/x64/loadlibrarycmd/windows/smb/x64/messageboxcmd/windows/smb/x64/meterpreter/bind_ipv6_tcpcmd/windows/smb/x64/meterpreter/bind_ipv6_tcp_uuidcmd/windows/smb/x64/meterpreter/bind_named_pipecmd/windows/smb/x64/meterpreter/bind_tcpcmd/windows/smb/x64/meterpreter/bind_tcp_rc4cmd/windows/smb/x64/meterpreter/bind_tcp_uuidcmd/windows/smb/x64/meterpreter/reverse_httpcmd/windows/smb/x64/meterpreter/reverse_httpscmd/windows/smb/x64/meterpreter/reverse_named_pipecmd/windows/smb/x64/meterpreter/reverse_tcpcmd/windows/smb/x64/meterpreter/reverse_tcp_rc4cmd/windows/smb/x64/meterpreter/reverse_tcp_uuidcmd/windows/smb/x64/meterpreter/reverse_winhttpcmd/windows/smb/x64/meterpreter/reverse_winhttpscmd/windows/smb/x64/meterpreter_bind_named_pipecmd/windows/smb/x64/meterpreter_bind_tcpcmd/windows/smb/x64/meterpreter_reverse_httpcmd/windows/smb/x64/meterpreter_reverse_httpscmd/windows/smb/x64/meterpreter_reverse_ipv6_tcpcmd/windows/smb/x64/meterpreter_reverse_tcpcmd/windows/smb/x64/peinject/bind_ipv6_tcpcmd/windows/smb/x64/peinject/bind_ipv6_tcp_uuidcmd/windows/smb/x64/peinject/bind_named_pipecmd/windows/smb/x64/peinject/bind_tcpcmd/windows/smb/x64/peinject/bind_tcp_rc4cmd/windows/smb/x64/peinject/bind_tcp_uuidcmd/windows/smb/x64/peinject/reverse_named_pipecmd/windows/smb/x64/peinject/reverse_tcpcmd/windows/smb/x64/peinject/reverse_tcp_rc4cmd/windows/smb/x64/peinject/reverse_tcp_uuidcmd/windows/smb/x64/pingback_reverse_tcpcmd/windows/smb/x64/powershell_bind_tcpcmd/windows/smb/x64/powershell_reverse_tcpcmd/windows/smb/x64/powershell_reverse_tcp_sslcmd/windows/smb/x64/shell/bind_ipv6_tcpcmd/windows/smb/x64/shell/bind_ipv6_tcp_uuidcmd/windows/smb/x64/shell/bind_named_pipecmd/windows/smb/x64/shell/bind_tcpcmd/windows/smb/x64/shell/bind_tcp_rc4cmd/windows/smb/x64/shell/bind_tcp_uuidcmd/windows/smb/x64/shell/reverse_tcpcmd/windows/smb/x64/shell/reverse_tcp_rc4cmd/windows/smb/x64/shell/reverse_tcp_uuidcmd/windows/smb/x64/shell_bind_tcpcmd/windows/smb/x64/shell_reverse_tcpcmd/windows/smb/x64/vncinject/bind_ipv6_tcpcmd/windows/smb/x64/vncinject/bind_ipv6_tcp_uuidcmd/windows/smb/x64/vncinject/bind_named_pipecmd/windows/smb/x64/vncinject/bind_tcpcmd/windows/smb/x64/vncinject/bind_tcp_rc4cmd/windows/smb/x64/vncinject/bind_tcp_uuidcmd/windows/smb/x64/vncinject/reverse_httpcmd/windows/smb/x64/vncinject/reverse_httpscmd/windows/smb/x64/vncinject/reverse_tcpcmd/windows/smb/x64/vncinject/reverse_tcp_rc4cmd/windows/smb/x64/vncinject/reverse_tcp_uuidcmd/windows/smb/x64/vncinject/reverse_winhttpcmd/windows/smb/x64/vncinject/reverse_winhttpsfeatures set postgres_session_type true.auxiliary/scanner/mssql/mssql_login module with a new CreateSession option which controls the opening of an interactive MSSQL session. This functionality is currently behind a feature flag which can be enabled with features set mssql_session_type true.features set mysql_session_type true.features set mssql_session_type true.dns command – a new command which mimics the functionality of /etc/resolv.conf and /etc/hosts. This functionality is currently behind a feature flag which can be enabled with features set dns_feature true in msfconsole.sqlcmd:post/windows/gather/credentials/mssql_local_hashdump and post/windows/manage/mssql_local_auth_bypass.exploit/linux/local/service_persistence when the payload is set to cmd/unix/reverse_netcat. The option to set the writable path is now BACKDOOR_PATH.exploit/windows/local/cve_2020_0787_bits_arbitrary_file_move module’s check method that was causing version comparisons to fail.exploit/windows/local/cve_2020_17136 module’s check method that was causing version comparisons to fail.exploit/windows/local/cve_2021_40449 module’s check method that was causing version comparisons to fail.exploit/windows/local/cve_2022_26904_superprofile module’s check method that was causing version comparisons to fail.auxiliary/scanner/mssql/mssql_login modules’s TDSENCRYPTION default value to false.help services or help hosts commands.windows/smb/psexec module was not correctly performing cleanup logic.You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.
As always, you can update to the latest Metasploit Framework with msfupdate
and you can get more details on the changes since the last blog post from
GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest.
To install fresh without using git, you can use the open-source-only Nightly Installers or the
commercial edition Metasploit Pro
Post Syndicated from Patrick Kennedy original https://www.servethehome.com/cloud-native-efficient-computing-is-the-way-in-2024-and-beyond-supermicro-intel-amd-ampere-nvidia/
Why cloud-native energy-efficient compute is the most exciting development for server CPUs since multi-core CPUs
The post Cloud Native Efficient Computing is the Way in 2024 and Beyond appeared first on ServeTheHome.
Post Syndicated from Ajinkya Patil original https://aws.amazon.com/blogs/security/how-to-automate-rule-management-for-aws-network-firewall/
AWS Network Firewall is a stateful managed network firewall and intrusion detection and prevention service designed for the Amazon Virtual Private Cloud (Amazon VPC). This post concentrates on automating rule updates in a central Network Firewall by using distributed firewall configurations. If you’re new to Network Firewall or seeking a technical background on rule management, see AWS Network Firewall – New Managed Firewall Service in VPC.
Network Firewall offers three deployment models: Distributed, centralized, and combined. Many customers opt for a centralized model to reduce costs. In this model, customers allocate the responsibility for managing the rulesets to the owners of the VPC infrastructure (spoke accounts) being protected, thereby shifting accountability and providing flexibility to the spoke accounts. Managing rulesets in a shared firewall policy generated from distributed input configurations of protected VPCs (spoke accounts) is challenging without proper input validation, state-management, and request throttling controls.
In this post, we show you how to automate firewall rule management within the central firewall using distributed firewall configurations spread across multiple AWS accounts. The anfw-automate solution provides input-validation, state-management, and throttling controls, reducing the update time for firewall rule changes from minutes to seconds. Additionally, the solution reduces operational costs, including rule management overhead while integrating seamlessly with the existing continuous integration and continuous delivery (CI/CD) processes.
For this walkthrough, the following prerequisites must be met:
In Network Firewall, each firewall endpoint connects to one firewall policy, which defines network traffic monitoring and filtering behavior. The details of the behavior are defined in rule groups — a reusable set of rules — for inspecting and handling network traffic. The rules in the rule groups provide the details for packet inspection and specify the actions to take when a packet matches the inspection criteria. Network Firewall uses a Suricata rules engine to process all stateful rules. Currently, you can create Suricata compatible or basic rules (such as domain list) in Network Firewall. We use Suricata compatible rule strings within this post to maintain maximum compatibility with most use cases.
Figure 1 describes how the anfw-automate solution uses the distributed firewall rule configurations to simplify rule management for multiple teams. The rules are validated, transformed, and stored in the central AWS Network Firewall policy. This solution isolates the rule generation to the spoke AWS accounts, but still uses a shared firewall policy and a central ANFW for traffic filtering. This approach grants the AWS spoke account owners the flexibility to manage their own firewall rules while maintaining the accountability for their rules in the firewall policy. The solution enables the central security team to validate and override user defined firewall rules before pushing them to the production firewall policy. The security team operating the central firewall can also define additional rules that are applied to all spoke accounts, thereby enforcing organization-wide security policies. The firewall rules are then compiled and applied to Network Firewall in seconds, providing near real-time response in scenarios involving critical security incidents.

Figure 1: Workflow launched by uploading a configuration file to the configuration (config) bucket
The Network Firewall firewall endpoints and anfw-automate solution are both deployed in the central account. The spoke accounts use the application for rule automation and the Network Firewall for traffic inspection.
As shown in Figure 1, each spoke account contains the following:
In the central account:
The input validations make sure that rules defined by one spoke account don’t impact the rules from other spoke accounts. The validations applied to the firewall rules can be updated and managed as needed based on your requirements. The rules created must follow a strict format, and deviation from the preceding rules will lead to the rejection of the request.
Rules not processed beyond the maxReceiveCount threshold are moved to a dead-letter SQS queue for troubleshooting.
The RuleExecute function also implements throttling controls to make sure that rules are applied to the firewall policy without reaching the ThrottlingException from Network Firewall (see common errors). The function also implements back-off logic to handle this exception. This throttling effect can happen if there are too many requests issued to the Network Firewall API.
The function makes cross-Region calls to Network Firewall based on the Region provided in the user configuration. There is no need to deploy the RuleExecute and RuleCollect Lambda functions in multiple Regions unless a use case warrants it.
The following section guides you through the deployment of the rules management engine.
In this phase, you deploy the application pipeline in the resource account. The pipeline is responsible for deploying multi-Region cross-account CDK stacks in both the central account and the delegated administrator account.
If you don’t have a functioning Network Firewall firewall using the centralized deployment model in the central account, see the README for instructions on deploying Amazon VPC and Network Firewall stacks before proceeding. You need to deploy the Network Firewall in centralized deployment in each Region and Availability Zone used by spoke account VPC infrastructure.
The application pipeline stack deploys three stacks in all configured Regions: LambdaStack and ServerlessStack in the central account and StacksetStack in the delegated administrator account. It’s recommended to deploy these stacks solely in the primary Region, given that the solution can effectively manage firewall policies across all supported Regions.

Figure 2: CloudFormation stacks deployed by the application pipeline
You can also deploy the spoke account stack manually for testing using the AWS CloudFormation template in templates/spoke-serverless-stack.yaml. This will create and configure the needed spoke account resources.

Figure 3: Example output of application pipeline deployment
After deploying the solution, each spoke account is required to configure stateful rules for every VPC in the configuration file and upload it to the S3 bucket. Each spoke account owner must verify the VPC’s connection to the firewall using the centralized deployment model. The configuration, presented in the YAML configuration language, might encompass multiple rule definitions. Each account must furnish one configuration file per VPC to establish accountability and non-repudiation.
Now that you’ve deployed the solution, follow the next steps to verify that it’s completed as expected, and then test the application.

Figure 4: Example configuration file for eu-west-1 Region

Figure 5: Example of logs generated by the anfw-automate in a spoke account

Figure 6: Rules created in Network Firewall rule group based on the configuration file in Figure 4
To avoid incurring future charges, remove all stacks and instances used in this walkthrough.
This solution simplifies network security by combining distributed ANFW firewall configurations in a centralized policy. Automated rule management can help reduce operational overhead, reduces firewall change request completion times from minutes to seconds, offloads security and operational mechanisms such as input validation, state-management, and request throttling, and enables central security teams to enforce global firewall rules without compromising on the flexibility of user-defined rulesets.
In addition to using this application through S3 bucket configuration management, you can integrate this tool with GitHub Actions into your CI/CD pipeline to upload the firewall rule configuration to an S3 bucket. By combining GitHub actions, you can automate configuration file updates with automated release pipeline checks, such as schema validation and manual approvals. This enables your team to maintain and change firewall rule definitions within your existing CI/CD processes and tools. You can go further by allowing access to the S3 bucket only through the CI/CD pipeline.
Finally, you can ingest the AWS Network Firewall logs into one of our partner solutions for security information and event management (SIEM), security monitoring, threat intelligence, and managed detection and response (MDR). You can launch automatic rule updates based on security events detected by these solutions, which can help reduce the response time for security events.
If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, contact AWS Support.