Security leaders today face a harsh reality: traditional vulnerability management isn’t enough. Threat actors are evolving, attack surfaces are expanding, and organizations need a more proactive approach to stay ahead of risk. Latest research from Gartner, How to Grow Vulnerability Management Into Exposure Management, highlights the need for security teams to move beyond simply tracking vulnerabilities and embrace a more comprehensive approach to exposure management.
At Rapid7, we are excited to offer complimentary access to this report and share our three key takeaways to help you modernize your security strategy.
Gartner states: “Creating prioritized lists of security vulnerabilities isn’t enough to cover all exposures or find actionable solutions. Security operations managers should go beyond vulnerability management and build a continuous threat exposure management program to more effectively scope and remediate exposures.”
CTEM shifts the focus from merely identifying vulnerabilities to understanding the full picture of organizational risk. It integrates asset visibility, business impact analysis, attack surface monitoring, and validation of security controls to help organizations assess and reduce their true exposure to threats.
Takeaway 2: Exposure Management Requires Business Context
One of the biggest challenges in vulnerability management today is that many security teams focus too much on discovering issues without evaluating their impact on the business. Gartner highlights the importance of integrating business context into security operations, stating that “adding a business context, such as asset value and impact of compromise, to exposure management activities can improve senior leadership engagement.”
By aligning security initiatives with business priorities, organizations can:
Focus on the vulnerabilities that pose the greatest risk to critical operations
Improve communication with senior leadership and stakeholders
Justify security investments with real business impact
Takeaway 3: Attack Surface Visibility Must Keep Up With Digital Evolution
Modern attack surfaces extend far beyond on-premises IT. The rise of cloud applications, IoT, supply chain dependencies, and remote work environments has dramatically increased the number of potential entry points for attackers. Gartner emphasizes that “current approaches to attack surface visibility are not keeping up with the rapid pace of digital evolution. Organizations must quickly reduce exposure to make their public-facing assets less visible and accessible.”
This means security teams need to enhance their discovery processes to:
Continuously monitor both their internal and external attack surface
Implement proactive security measures to reduce overall exposure
How Rapid7 Aligns with Gartner Exposure Management Vision
At Rapid7, we believe in empowering security teams with the tools and insights they need to shift from reactive vulnerability management to proactive exposure management. Our Exposure Management solution helps organizations:
Gain real-time visibility into evolving attack surfaces
Prioritize threats based on business impact and exploitability
Continuously validate security controls through adversarial exposure testing
As threats continue to evolve, organizations must rethink how they approach vulnerability management. Gartner research provides a roadmap for security leaders looking to implement a comprehensive exposure management strategy.
Garter, How to Grow Vulnerability Management Into Exposure Management, Michell Schneider, Jeremy D’Hoinne, Jonathan Nunez, Craig Lawson, 8 November 2024
GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved.
Co-authored by Peter Whibley, Ed Montgomery, and Joel Alcon
Technology innovation combined with the highly fragmented nature of today’s IT landscape means that vulnerabilities are being exploited faster and at greater scale than ever. Security teams contend with a daily surge of new threat actors and attack vectors. Without a unified view of assets, business context, and compensating controls, they waste weeks identifying which risks are truly critical.
Many organizations try to tackle this challenge by implementing exposure management and risk-based vulnerability management (RBVM) approaches, where vulnerability data from various tools is consolidated into one dashboard. But many of these tools present risk scores without demonstrating a holistic view of the business impact of vulnerabilities, mitigating controls for endpoints, patch management status, and remediation steps.
Without that end-to-end context, security teams are struggling to keep up with the volume of new vulnerabilities. In fact, once the National Vulnerability Database (NVD) announced in February 2024 that it would no longer provide vulnerability scores for all CVEs, the shortcomings of traditional vulnerability management, including RBVM, became more evident.
From chasing vulnerabilities, to proactively mitigating risk
Rapid7’s Remediation Hub enables security teams to go beyond simply identifying vulnerabilities and focus more on remediating risk. By augmenting vulnerability findings with business context, threat intelligence, and compensating controls, organizations gain a continuous, all-in-one view of how to detect and respond to risks across their enterprise. These new capabilities empower security teams to:
Assess the impact of remediation steps. Reimagine your attack surface by viewing the number of vulnerabilities addressed by each remediation action.
Prioritize remediation with confidence. Leverage dynamic, threat-aware risk scores to assess the criticality of issues and quickly go from vulnerability to action.
Optimize risk mitigation. Accelerate risk response through streamlined remediation workflows.
Security teams leverage multiple vulnerability scanning tools for different parts of their infrastructure, including cloud environments, containers, web applications, and endpoints. Each tool reports findings in its own format and utilizes different scoring methods, making it difficult to get a clear, unified picture of an organization’s risk exposure.
By unifying this data into a centralized platform, security teams reduce unnecessary noise caused by redundant vulnerability findings, streamlining triage efforts, reducing silos, and driving faster, more informed remediation efforts.
Rapid7 Remediation Hub delivers this normalized view of third-party vulnerabilities, enabling teams to stop wasting time chasing low-impact issues or overlook high-severity threats. The solution takes this unified lens further via risk scores that combine these vulnerability findings with business context to help security teams quickly identify the most critical vulnerabilities, allocate resources efficiently, and communicate risk more effectively to stakeholders. These capabilities not only boost operational efficiency, but also strengthen an organization’s security posture.
Context-based visibility into endpoint protection and patch management
Context is an essential component of managing risk in today’s increasingly complex technology landscape. By solely relying on vulnerability scores without also understanding business impact or breach likelihood, security teams are left with a hazy, incomplete view of their attack surface.
Rapid7 Exposure Command empowers security teams to prioritize vulnerabilities based on attacker behavior, exploitability, and potential impact – all without the need to export data into separate security tools. Rapid7 delivers deep, multi-layered risk scores calculated from Rapid7 Labs’s threat intelligence, first-party scans, third-party vulnerability findings, and an organization’s unique mitigating controls. Furthermore, Remediation Hub is seamlessly integrated with Rapid7 Surface Command, arming security teams with a continuous view of key mitigating controls of assets across the enterprise, including endpoint protection and patch management in place.
Endpoint protection – Remediation Hub displays which assets have active endpoint protection, as well as the protection type on the asset. Users can use intuitive filters to hone in on critical findings, such as the assets that lack endpoint protection and prioritize remediation efforts via a risk-based approach that gives higher priority to assets that lack endpoint protection.
Patch management – Remediation Hub shows the patch management availability status of each asset, arming security teams with a view of assets that are available for patching by a patch management system. Users can filter on assets with vulnerabilities where no patching is active.
Faster risk response, fewer security silos
Security teams often operate in silos, with a team handling risk identification and another focused on remediation. CISA recommends that critical vulnerabilities be remediated within 15 calendar days of initial detection, but to achieve this, organizations require tight collaboration between these disparate teams.
Unfortunately, because these groups operate with poorly integrated security tools, going from vulnerability finding to risk remediation can take months, with some vulnerabilities going unpatched for years. For instance, the 2024 Verizon Data Breach Investigations Report finds that it takes an estimated 55 days to remediate 50% of critical vulnerabilities once their patches are available.
Remediation Hub tackles this challenge with purpose-built SOAR integrations that help improve collaboration and drive down MTTR (mean time to remediate). The new capabilities automatically trigger remediation workflows, with notifications auto-generated and sent to adjacent teams responsible for implementing the recommended remediations.
For example, users can leverage Remediation Hub to automatically trigger a workflow in Jira or create an incident report in ServiceNow based on the severity or business impact of a vulnerability. Each workflow is fully customizable based on unique security thresholds.
Embracing faster, continuous exposure management
Organizations are rapidly transitioning from traditional vulnerability management to more continuous, exposure management approaches. Rapid7’s Remediation Hub – an integral component of the Exposure Command platform – empowers security teams to embrace the shift.
With a remediation-based approach to vulnerability management and risk reduction, organizations are taking command of their attack surface and discovering a simpler, more effective approach to managing and truly mitigating risk.
If you are interested in learning more about Remediation Hub and our Exposure Command platform, check out our Exposure Command product tour.
When it comes to defending your organization, every second counts. The time to detect, respond, and remediate is critical, but speed alone isn’t enough. Fragmentation across security tools, siloed teams, and manual workflows leaves organizations constantly reactive, overwhelmed by alerts, and at risk of breaches. Rapid7 is here to change that.
Organizations need solutions that unify their approach, streamline processes, and accelerate response times. Rapid7 delivers the industry’s broadest, most unified view of the attack and detection surface. Today, we’re thrilled to announce a series of strategic launches that further this integrated approach and deliver unified remediation across the full breach timeline, integrating proactive exposure management with intelligent detection and automated response. This comprehensive approach provides security teams with the precise tools and deep insights needed to effectively secure their organization and shift from proactively reducing vulnerabilities to swiftly resolving active threats.
Left of Boom: Proactive Exposure Remediation
The most effective security strategy begins before a breach ever happens. Rapid7’s Exposure Command directly addresses this gap, combining advanced risk-based vulnerability management (RBVM) with environmental context, threat intelligence, and native workflow automation.
Launching this week at RSA, we’re excited to announce a trio of updates to Remediation Hub aimed at helping organizations unify and modernize their vulnerability management programs:
Enhanced Automated Remediation Workflows: We’ve significantly expanded our workflow automation capabilities to streamline exposure remediation. Users can now easily launch both pre-built and fully customizable remediation workflows—including notifications, ticketing, and patch deployment—directly from the intuitive Remediation Hub interface. This seamless integration simplifies the remediation process, allowing teams to swiftly address vulnerabilities and maintain robust security hygiene.
Advanced Compensating Controls Assessment: Remediation Hub now provides comprehensive insights into existing compensating controls, empowering teams to strategically deprioritize vulnerabilities that present minimal or no practical risk due to limited accessibility or exploitability—such as a compromised asset running antivirus or behavior prevention. This enhanced visibility is particularly vital for managing unpatchable workloads or addressing vulnerabilities where patches or permanent fixes are currently unavailable.
Expanded Third-Party Vulnerability Integration: Exposure Command has always integrated valuable telemetry from third-party vulnerability scanners such as Tenable, Qualys, and Wiz. Now, we’ve enhanced this capability by incorporating vulnerability findings and detailed risk scoring directly into the Remediation Hub. This allows vulnerabilities identified from any 3rd-party integration to be effectively prioritized using Active Risk assessments and effortlessly embedded into your team’s existing remediation and patch management workflows, streamlining vulnerability management across diverse scanning solutions.
With these new enhancements to Remediation Hub, security teams are empowered with a real-time, validated understanding of exposures enriched with business context, adversary intelligence, and insight into existing compensating controls, not just a list of CVEs. And because the Exposure Command platform brings together native scanning from Rapid7 and vulnerability findings from third-party tools, teams can prioritize vulnerabilities based on attacker behavior, exploitability, and potential impact without spending valuable time porting data into separate tools.
Instead of just alerting your team to a vulnerability, Exposure Command helps you own the risk conversation with the business by aligning on what matters most to the business, the risks already addressed, and outlining a path to closing any remaining gaps. Security teams no longer have to guess which vulnerabilities pose the most risk; instead, they can proactively remediate with certainty, preventing vulnerabilities from escalating into incidents.
Right of Boom: Intelligent Detection, Confident Response, and Financial Assurance
Despite best efforts, security incidents and breaches are ever-present. To reduce their impact and the cost of remediation, security teams need rapid, intelligent responses to evolving incidents, helping them to prioritize and triage, and leverage automation to reduce the volume of potential investigations, and improve their ability to scale to meet remediation tasks. This is why Rapid7 is focusing efforts around building in support post event, marking a significant shift in our capabilities to remediate malicious attacker behavior:
AI Triage and Transparency within InsightIDR: Rapid7 was a pioneer in AI development for security use cases, starting in our earliest days with our VM Expert System in the early 2000s. Since then, Rapid7 has integrated Generative AI into the Command Platform to supercharge SecOps and augment MDR services. This has culminated in Rapid7’s AI-Assisted Triage delivering industry-leading precision, accurately distinguishing critical threats from benign alerts with a 99.89% accuracy rate. Without access to the Rapid7 AI Alert Triage capability, SOC teams waste significant time manually evaluating and correctly classifying malicious alerts, increasing their threat exposure and contributing to SOC inefficiency. With AI Alert Triage, SOC analysts can automatically and accurately focus limited security resources on legitimate threats and improve SOC performance.
Active Remediation with Velociraptor: The response capabilities of the Rapid7 SOC have expanded to include the swift and precise removal of malware and breach artifacts from impacted endpoints. This progression beyond remote containment and guided remediation represents a significant deepening of the MDR partnership between Rapid7 and customers. It relieves security teams not only from the burden of coordinating remediation actions with IT teams, but also helps preserve endpoint integrity, reduce downtime, and avoid unnecessary endpoint rebuilds. With real-time remediation capabilities, the Command Platform links actions directly back to known vulnerabilities, providing valuable context for future prevention and significantly shortening incident response cycles.
Breach Protection Warranty: Investing in security solutions is about more than technology and expert service delivery. It’s about guaranteed results and peace of mind. The Rapid7 SOC analyzes trillions of events each year, and 99.6% of MDR customers remain unaffected by ransomware. Recognizing this, and reinforcing our commitment to ensuring cybersecurity resilience, customers in our premium tier, Managed Threat Complete Ultimate, will now receive up to $1 million in breach-related financial coverage through our Breach Protection Warranty. This represents a tangible demonstration of our confidence in our solutions and our commitment to protecting your organization’s critical assets while also assuring you that, in the unlikely event of a compromise, we are right there by your side.
As our detection and response capabilities continue to expand, we’re pushing to deliver smarter, faster, and more complete security outcomes for our customers. With alert fatigue diminished through precise AI-Assisted Alert Triage, security analysts can spend more time on validated threats and strategic initiatives to enhance organizational posture. The expansion of Rapid7’s response workflow to include remediation redefines effective response while ensuring customer visibility and control. And now, our Breach Protection Warranty offers up to $1 million in breach-related financial coverage: we’re not just preventing and helping you recover from threats, we’re standing behind our ability to do so. Together, these capabilities mark a meaningful shift in how Rapid7 supports customers post-incident: with intelligence, speed, and confidence that extends all the way through recovery.
One Connected Journey, End-to-End
Cybersecurity incidents are complex, evolving threats requiring seamless integration of proactive and reactive security measures. Rapid7’s Command Platform bridges the traditional divides between proactive vulnerability management, intelligent threat detection, and automated incident remediation. With a unified, continuous security lifecycle, your organization can remain agile, informed, and resilient against emerging threats.
Take your cybersecurity posture to the next level. Discover how Rapid7’s unified remediation strategy delivers measurable results and helps secure your organization effectively against breaches. Interested in learning more about how Rapid7’s unified remediation strategy can transform your organization’s security posture? Learn more here.
Cybersecurity threats are evolving at an unprecedented pace, making it imperative for organizations to stay ahead of attackers with proactive security measures. To help organizations navigate this rapidly changing threat landscape, we are excited to introduce the Exposure Assessment Platform (EAP) Buyer’s Guide. This comprehensive guide is designed to help security professionals understand the critical role of EAPs in modern security programs, evaluate potential solutions, and implement the right tool for their organization.
Why you need an EAP
Exposure Assessment Platforms (EAPs) continuously identify and prioritize exposures, such as vulnerabilities and misconfigurations, across a broad range of asset classes. EAPs go beyond traditional vulnerability management by offering real-time visibility into an organization’s entire IT environment, enabling security teams to proactively mitigate risks and prioritize remediation efforts effectively.
An EAP is a critical component of a Continuous Threat Exposure Management (CTEM) program. With this in mind, our buyer’s guide provides essential insights into:
The importance of EAPs in modern security strategies
How EAPs support a CTEM framework
Key criteria to consider when evaluating an EAP solution
Best practices for implementing continuous risk management
How to evaluate and find the right EAP
Not all EAPs are created equal. When assessing potential solutions, organizations should prioritize platforms that offer:
Comprehensive visibility across all digital assets, including cloud environments, third-party integrations, and IoT devices.
Real-time continuous monitoring to detect new vulnerabilities and attack vectors.
Automated security testing and validation to assess real-world exploitability.
Seamless integration with existing security tools to enhance threat intelligence and remediation workflows.
How Rapid7’s EAP can help strengthen your security
For organizations looking to gain complete control over their attack surface, Rapid7’s Exposure Command offers unparalleled visibility and risk assessment capabilities. By aggregating insights from native exposure detection and third-party sources, Exposure Command enables security teams to:
Identify and prioritize vulnerabilities based on real-world threat intelligence to reduce blind spots and misconfigurations.
Integrate with existing security ecosystems, reducing operational overhead.
Increase ROI by tracking the impact of reducing risk exposure across the business in real time.
With Rapid7 Exposure Command, organizations can reduce manual efforts, optimize security workflows, and proactively mitigate risks before they escalate into breaches. And by leveraging the insights and best practices outlined in this guide, organizations can make informed decisions to enhance their security posture, mitigate risk, and stay ahead of emerging threats.
In traditional conflicts, intelligence is both integral and beneficial to decision-making at every level. Unfortunately, in cybersecurity, the impact of threat intelligence as an asset for organizations—and in particular their security operations team—has been less significant.
Why has this been the case? While threat intelligence should be intrinsic to the detection and response process, the reality is that security teams are overwhelmed with far too much noise to efficiently gather what they need from it. Not responding in a timely fashion ultimately means that by the time any response can be mustered, it will be too late. This is particularly the case given threat actors’ dwell times have in some instances decreased to a matter of hours.
The threat landscape is not static—defenders need a continuous view of what is occurring, right now.
We are delighted to announce the availability of Intelligence Hub, an evolution in threat intelligence delivery that is designed to provide meaningful context and actionable insights integrated with the Rapid7 Command Platform.
High-fidelity data: curated intelligence
Intelligence is not a commodity. Simply gathering every feed is why many organizations are overwhelmed and unable to respond in a timely manner to disrupt the kill chain before attackers move to the final stage. Consider many of the recent significant breaches; invariably, alerts are missed and data is exfiltrated. With this in mind, the focus of Rapid7 Labs has been to increase the fidelity of data, leveraging our own approach to curated intelligence.
Data that can be trusted
The objective of curated intelligence is to extract the low-prevalence indicators and verify the malicious nature of the artifact, thus enabling a timely response while reducing the risk of false positives. Introducing high-fidelity data also provides the opportunity to automate the response. Such an approach goes beyond the analyst and considers what an appropriate response should be.
The curated intelligence within Intelligence Hub is derived from ingestion sources that are unique to Rapid7, such as our honeypot data and proprietary research, as well as insights from our open source and research communities. These include Metasploit, AttackerKB, and other global communities that make our reach into understanding the threatscape both broader and deeper. Expertly crafted machine learning (ML) models combined with manual verification from our Rapid7 Labs team create additional layers of validation.
What matters to me? Understand prevalence quickly with the campaigns that are targeting your business sector or geography as efficiently as possible.
Decay modeling maintains relevance
Even curated intelligence can quickly get very stale. If we consider an IP address used within a given campaign, this artifact will soon cease to be relevant since threat actors will migrate once it has been identified as known bad. For this reason, Intelligence Hub shows the decay score, which will reduce over time as the artifact migrates from known bad to unknown (or another state).
A view of campaign activities being conducted by the Mustang Panda APT group (correct at the time of writing). Intelligence Hub covers all major threat activities from organized crime and APT groups.
Contextualized information
Intelligence Hub’s higher fidelity data remains continuously updated, allowing us to move away from the problem of traditional Threat Intelligence Platforms (TIPs) that have provided the firehose of false positives and noisy alerts. The opportunity is to now use prevalence to allocate resources to only the areas which are necessary. In other words, if a threat campaign is targeting a specific sector and/or geography and exploiting specific vulnerabilities, then surely these will require remediation first. In addition, if the campaign is being carried out by a ransomware group whose dwell time continues to drop, then almost certainly prioritizing remediation should include automation.
Automation does, of course, demand high-fidelity data, which is why curated intelligence remains the foundation of the solution.
Actionable insights
What all of this means is the security teams can get true, actionable insights — understanding what indicators within their environment are confirmed as malicious, as well as the threat actors’ motivations. Utilizing these insights to take the appropriate action to mitigate the threat in a timely fashion now becomes a reality with Intelligence Hub.
Learn more about the active threat groups conducting operations in the world today.
Intelligence is great, but what does this mean for your organization?
Above all else, the integration of Intelligence Hub with the Rapid7 Command Platform provides the ability to go beyond the analyst and deliver true security outcomes. Firstly, with our next-gen SIEM, Rapid7 InsightIDR, the security analyst can prioritize triaging security alerts that demand attention. For example, if there are reliable indicators regarding the possibility of a ransomware group inside the environment, this clearly demands prioritization with the intention of disrupting the kill chain before the final stage payload is delivered. Such an approach reinforces why context matters, and perhaps controversially, why attribution becomes operationally relevant.
Migrate away from the dependency of manual tools to integrate intelligence into operations and surface the alerts that truly matter.
Threat-informed remediation: beyond the security analyst
The role of intelligence Hub therefore goes beyond the security analyst, and supports integration with the remediation actions of any organization. An upcoming integration with Remediation Hub will give security analysts the added insight to justify security updates being rolled out outside of the normal change control cycle. An example of this could be CVE-2024-55591, an authentication bypass in Fortinet firewalls, which was exploited as a zero-day in January 2025 and reported to be used by ransomware groups on March 18, 2025. This attack warrants immediate remediation in order to mitigate the potential of being exploited. This answers the question many security practitioners are often asked: Are we vulnerable? And, with the investigation option within Intelligence Hub, the opportunity exists to answer the question: Have we been compromised?
With actionable (and relevant) intelligence being incorporated into the allocation of resources for remediation, Intelligence Hub provides the critical data necessary for effective security operations.
Intelligence Hub is the integrated threat intelligence solution that delivers proactive context and prioritization, rapidly accelerating time to remediation.
The evolution of threat intelligence
In summary, Intelligence Hub represents a significant leap forward in threat intelligence delivery. By providing curated, high-fidelity data with relevant context and actionable insights, it empowers security teams to move beyond the noise of traditional threat intelligence solutions. The integration with the Rapid7 Command Platform and Remediation Hub further offers threat-informed remediation, allowing organizations to prioritize and automate responses effectively. Ultimately, Intelligence Hub is designed to help organizations achieve true security outcomes by focusing on what truly matters and disrupting the kill chain quicker, and with greater confidence. Learn more about Intelligence Hub here.
The live sessions may be over, but with every talk now available on demand, it’s the perfect time to reflect on the biggest takeaways from this year’s summit—and how they can help security teams move faster, act smarter, and take control of their attack surface.
From red teaming tactics to regulatory readiness, here are some of the standout lessons and ideas shared by speakers across the day.
1. Red Teaming Isn’t Just About Getting In—It’s About What Happens Next
In Outpacing the Adversary, Aaron Herndon, Senior Director, Sales Engineering at Rapid7 and Will Hunt, Co-Founder of In.security, reminded us that red teaming isn’t just about proving a breach is possible. It’s about helping teams understand how attackers think, where they’re likely to go, and whether detection and response controls actually work in practice.
From creative simulations to critical discussions on ethical boundaries and scope, the message was clear: red teaming is most valuable when it drives real organizational learning.
2. You Can’t Prioritize What You Can’t See
In Risk Revolution: Proactive Strategies forExposure Management, panelists from Rapid7 and ESG made it clear that visibility remains the top challenge for most teams. Fragmented data, sprawling assets, and misaligned priorities are slowing teams down.
The solution? A unified, risk-aware approach to exposure management—one that considers cloud, identity, data, and application risk in context. Prioritization must reflect business reality, not just vulnerability severity.
3. Cloud Security Requires Context
In DemystifyingCloud Detection & Response, panelists shared how traditional tools aren’t built for dynamic, cloud-native environments. Logs are short-lived, workloads are ephemeral, and identity is often the weakest link.
To respond effectively, SOC teams need visibility, automation, and integrations that bring context across systems. The modern attack surface starts well before the endpoint.
4. Compliance Is Evolving. It’s Not a Checkbox Exercise
From Chaos to Compliantbrought practical guidance for navigating frameworks like NIS2, DORA, and SEC cyber rules, among others. The takeaway? Compliance and security are strongest when they work together.
With the right tools, processes, and internal alignment, compliance can become a strategic advantage—not just a box to tick.
5. AI Is Here. Use It Thoughtfully
AI was a recurring theme throughout the day, especially in AI in Action. Rapid7’s engineering and product teams showcased how they’re applying AI across triage, prioritization, and detection, while keeping responsible deployment top of mind.
The takeaway: AI can boost speed and scale, but human oversight and thoughtful governance are still essential.
6. Visibility Gaps Are Where Attackers Thrive
In Inside the SOC, Rapid7 threat hunters shared stories of real-world breaches where attackers operated undetected due to logging gaps, missing coverage, or misconfigured systems.
Whether it’s credential theft through Microsoft Teams impersonation attacks or ransomware in unmanaged environments, the message was clear: you need full visibility to stay ahead.
7. Security Is a Team Sport
Across sessions—from exposure management to cloud strategy to customer-led discussions—one thing was clear: effective security requires collaboration.
Security teams, IT, engineering, and compliance all need shared context and coordinated goals to defend today’s growing attack surface.
Catch Up or Rewatch: All Sessions On Demand
Every session from Take Command 2025 is now available to watch. Whether you missed one or want to revisit a discussion with your team, you can dive back in anytime.
On April 16, CISA extended funding to ensure no continuity issues with the critical Common Vulnerabilities and Exposures (CVE) program. This was in response to a letter sent by MITRE on April 15 to CVE board members warning of a potential issue with MITRE’s support for the CVE program. MITRE administers the global CVE program, which provides the human and technological infrastructure to reserve, publish, modify, and dispute CVEs.
Rapid7 continues to monitor both public and private discussions closely in its capacity as a CVE Numbering Authority (CNA) and as a longtime leader and participant in the CVE ecosystem.
How this could impact Rapid7 and our customers
Since funding has been extended for the next 11 months, there is no current impact. Rapid7 will continue to monitor the situation to ensure there is no future impact to our customers’ ability to use our platform to accurately assess their environment for vulnerabilities.
Rapid7’s multi-layered approach to vulnerability detection, creation, and risk scoring means that our products are not completely reliant on any single source of information. This was something we pointed to last year, when we assured customers of our continued vulnerability coverage in the face of NIST’s National Vulnerability Database delays.
The importance of MITRE and the CVE Program
The CVE program is critical infrastructure for modern vulnerability identification, tracking, management, and resolution. CVEs are used for risk identification, commercial and open-source tooling, vulnerability management workflows, security and academic research, threat intel production, incident response, and many other applications worldwide.
Rapid7 thanks and supports the MITRE organization as well as the extended ecosystem of industry collaborators who have worked diligently for the past 25 years to ensure the CVE program’s utility and integrity for the broader community.
We will continue to monitor the situation and will update this blog with any relevant developments. If you have any questions, please reach out.
Take Command 2025 is officially in the books. From the opening sessions to the final takeaways, the summit delivered a full day of high-impact discussions, fresh research, and powerful stories from across the cybersecurity spectrum.
This year’s event brought together cybersecurity leaders, researchers, red teamers, and policy experts for an honest look at the challenges we’re facing—and the tools, tactics, and mindsets helping us take command in a complex threat landscape.
We’re grateful to everyone who joined us and proud of the conversations that unfolded throughout the day. If you missed any sessions or want to rewatch key moments, every session is now available on demand.
A Day of Firsts: New Research, New Tools, Real Stories
One of the standout moments came during Inside the Mind of an Attacker: Navigating the Threat Horizon session, where Raj Samani and Trent Teyema previewed findings from Rapid7’s latest ransomware intelligence. Based on data from Q1 2025, the discussion touched on shifting attacker tactics, the growing professionalism of ransomware groups, and the need for visibility and response readiness at every level.
Another highlight was Ted Harrington’s keynote, From Zero to Hero: Building the Perfect Defense, which challenged us to reimagine security architecture from the ground up. Ted emphasized bold thinking, Zero Trust foundations, and security’s role as a business enabler—not a roadblock.
In Risk Revolution: Proactive Strategies for Exposure Management, speakers laid out practical frameworks for prioritizing risk across cloud, identity, data, and application layers. And in Demystifying Cloud Detection & Response, panelists explored how SOC teams can bridge traditional and cloud-native security gaps using the right integrations and context-rich telemetry.
We also heard from customer leaders during Expert Tips to Future-Proof Your VM Program, where panelists from Cross Financial, Miltenyi Biotec, and Phibro Animal Health discussed the shift from vulnerability management to exposure-led strategies.
Compliance, Resilience, and Looking Ahead
With global regulations evolving fast, From Chaos to Compliantsession offered clear, actionable guidance for navigating global compliance legislations, such as SEC, NIS2, and DORA amongst many others—without compromising operational efficiency. Sabeen Malik and Lara Sunday reminded us that compliance, done right, can be a catalyst for organizational resilience.
And in one of the most engaging sessions of the day, The Tempest Two shared stories of adventure and mindset that resonated with security teams striving to adapt, overcome, and lead with purpose in high-pressure environments.
Now Streaming: All Sessions On Demand
Couldn’t attend live—or want to revisit a key session? Every session from Take Command 2025 is now available to watch on demand. Whether you’re catching up or sharing with your team, this is your chance to revisit the insights and strategies shaping the future of cybersecurity.
Take Command 2025 is just two days away, and there’s still time to secure your spot. Whether you’ve already registered or are building your agenda now, there’s plenty to look forward to — and it all starts this Wednesday, April 9.
In the lead-up to the live summit, two new on-demand sessions are already available for viewing, giving you a head start on key themes like attacker behavior and regulatory change. And during the event itself, you’ll get an exclusive look at findings from Rapid7’s latest ransomware research — pulled directly from Q1 threat activity and shared publicly for the first time.
This year’s event brings together top minds in cybersecurity for a full day of insights on exposure management, MDR, AI ,threat intelligence, red teaming, and more. It’s practical, high-impact content designed for practitioners, team leaders, and CISOs alike.
Hear the Latest Findings First at Take Command
If you want a pulse check on what’s happening across the threat landscape, don’t miss Inside the Mind of an Attacker: Navigating the Threat Horizon, led by Raj Samani, Chief Scientist at Rapid7.
Raj will be joined by Trent Teyema, Founder of CSG Strategies and former head of the FBI Cyber Division, for a panel that explores attacker methodologies, tactics, and trends. During the session, Raj will share key findings from Rapid7’s latest ransomware research, which will add depth to this important and insightful discussion. Attend this session and you’ll get a special research infographic and link to the detailed blog, which dives into
Which ransomware groups are most active in 2025 so far
How pressure tactics and extortion models are evolving
Which industries are being targeted — and why
What security teams can do now to reduce risk
Still Time to Register
There’s still time to register and experience Take Command 2025 as it happens. Attending live means you’ll:
Ask your questions during real-time Q&As
Hear fresh research and insights as they’re shared
Connect with experts and peers across the industry
This is your chance to be part of the conversation — not just watch it later. And if your schedule shifts? All sessions will be available on-demand after the event, so you can catch up at your convenience.
Get Ready to Take Command
Take Command 2025 brings together frontline experience, original research, and actionable guidance — all in one virtual event. If you haven’t registered yet, now is the time.
Whether you’re joining live, watching on-demand, or getting a head start with early sessions, this is your opportunity to learn what today’s threats really look like — and how to stay ahead of them.
Take Command 2025 is packed with insights from cybersecurity experts, threat intelligence leaders, and hands-on practitioners. But you don’t have to wait until April 9 to start learning. Two exclusive sessions are now available on-demand — giving you early access to critical content designed to help you think like an attacker, respond like a pro, and prepare for what’s next.
Whether you’re in the trenches of daily operations or shaping security strategy at the executive level, here’s what’s in it for you — and why attending Take Command 2025 is a must.
Start Learning Now: Two Must-Watch Sessions, Now On-Demand
Demo: How Hackers Think – The Anatomy of a Real-World Attack.
Want to see how attackers operate in the real world — and how to stop them? In this hands-on demo, Zachary Jones, Senior Security Solutions Engineer at Rapid7, walks through the anatomy of a real-world cyberattack.
You’ll follow the attacker’s journey from initial access to exploitation, seeing how vulnerabilities are identified and used — and how proactive defenses can stop them in their tracks. This session is a great primer ahead of the event for teams looking to better understand attacker behavior and refine detection strategies.
Watch the session on-demand now and come to Take Command 2025 with a sharper perspective on how to defend against what you’ll face next.
From Chaos to Compliant: Demystifying Cyber Regulations
Cyber regulations aren’t just growing — they’re shifting fast. This session unpacks the global compliance landscape and explores how security leaders can turn policy change into security strength.
Led by Ellis Fincham, EMEA Threat & XDR Sales Specialist Lead at Rapid7, the panel features Lara Sunday, Product Manager at Rapid7, and Sabeen Malik, VP of Global Government Affairs & Public Policy. Together, they provide real-world context on evolving frameworks like NIS2 and DORA, how to adapt to ongoing regulatory pressure, and what global organizations should consider when it comes to regional SaaS deployments and data residency requirements.
If you’re a CISO, compliance lead, or just trying to stay ahead of the next policy shift — this is one to bookmark.
This year’s event is built to give you practical guidance you can apply right away — whether you’re leading a security program, managing a team, or defending the frontlines.
Here’s what’s in store:
Expert-led panels and technical sessions on AI, MDR, threat intelligence, exposure management, red teaming, and more
Exclusive industry perspectives from Rapid7 researchers, product leaders, and global policy experts
On-demand content before and after the event, so you can engage on your terms
It’s everything you need to command your attack surface with confidence.
Take Command Starts Now
Take Command 2025 goes live on April 9, but you can start learning today. Watch both sessions now on-demand and get ready for a full day of insights that will move your security strategy forward.
A Rebirth of a Cursed Existence? Examining ‘Babuk Locker 2.0’ Ransomware
Introduction
Ransomware remains a major threat, causing significant disruption and financial losses to organizations across various sectors. Cybercriminal groups behind these attacks constantly adapt their methods to maximize damage and profit.
At Rapid7, we actively monitor new cyber threats, keeping an eye on ransomware groups and their changing tactics. In early 2025, we came across a channel promoting itself as Babuk Locker. Since the original group had shut down in 2021, we decided to investigate whether this was a rebrand or a new threat. Several underground forums and Telegram channels started mentioning ‘Babuk Locker 2.0,’ with some actors taking credit for recent attacks. Since Babuk’s leaked source code in 2021 had led to many spin-off ransomware strains, we wanted to find out whether this was a real comeback or just another group using Babuk’s name.
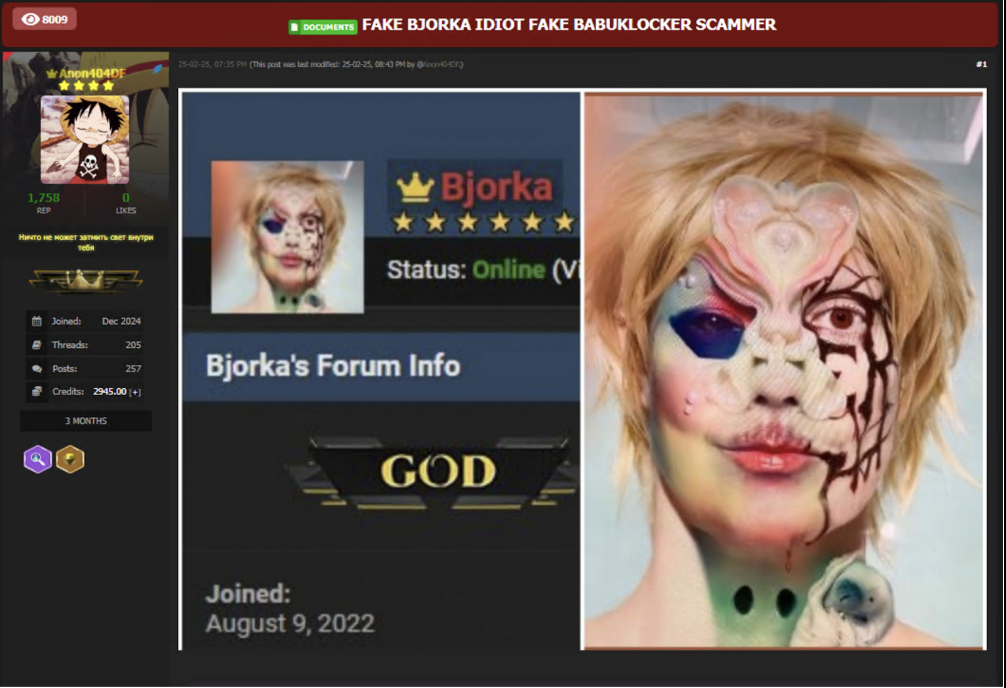
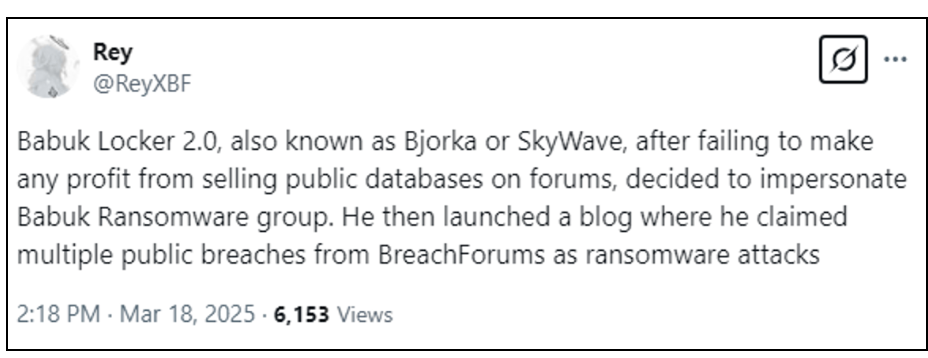
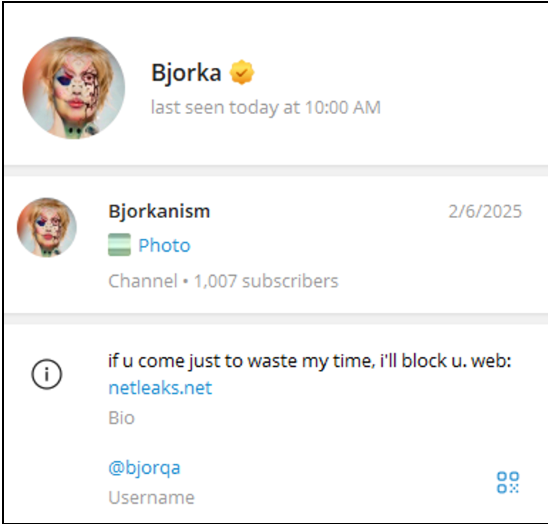
Figure 1 – Online discourse against Bjorka as a scammerFigure 2 – Online discourse against Bjorka and SkyWave as scammers
We started by gathering intelligence from dark web marketplaces, hacker forums, and private Telegram groups. We saw a rise in discussions about Babuk’s return, often linked to two groups, ‘Skywave’ and ‘Bjorka.’ These actors claimed responsibility for major attacks, and their leak sites suggested they might be working with other cybercriminal groups.
This blog delves into the potential revival of Babuk Locker 2.0, its alleged operators, and their activities. We analyze the involvement of ‘Skywave’ and ‘Bjorka,’ their claimed victims, and the evolution of Babuk’s Ransomware-as-a-Service (RaaS) model. Our findings include technical analysis, victimology, and the broader risks posed by this campaign.
Operators: Skywave and Bjorka
While monitoring Babuk Locker 2.0 activity, we identified two key groups linked to its operations—Skywave and Bjorka. These groups frequently appeared in discussions on underground forums and Telegram channels, claiming responsibility for attacks and promoting Babuk-related leaks. Our analysis suggests that these groups play a significant role in Babuk Locker 2.0’s activities, either as affiliates or key operators.
Skywave
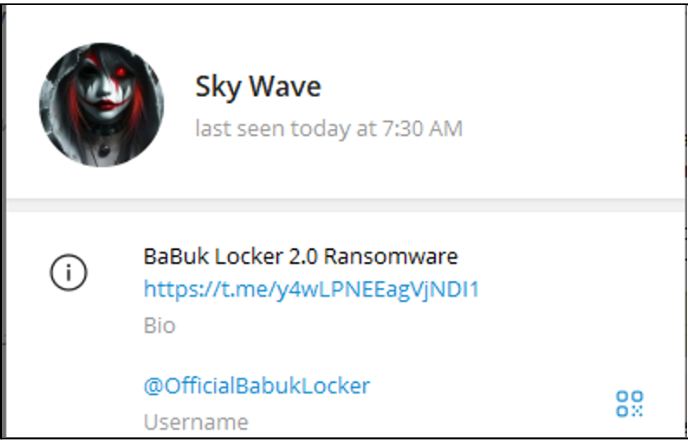
Skywave is a recently identified threat actor known for allegedly executing cyberattacks against various high-profile organizations and government agencies. Their operations have raised concerns within the cybersecurity community due to the sensitivity and volume of the data reportedly compromised, as well as the anonymity of the operator. Skywave is suspected of operating multiple Telegram channels under different aliases, some of which have been flagged as scams and removed by Telegram.
The specific TTPs employed by Skywave remain undisclosed, leaving room for speculation regarding their infiltration and data exfiltration methods. Since late 2024, Skywave has maintained its presence on various platforms, such as Telegram, DarkForums, and the dedicated Babuk Locker 2.0 DLS, where they have been sharing leaked data from their allegedly recent attacks. Victim lists indicate a focus on high-profile organizations with sensitive data.
Figure 3 – The Telegram user of Skywave
Bjorka
Bjorka is a threat actor mainly known for allegedly breaching Indonesian government and citizen data, often leaking sensitive information as a form of hacktivism. The alias gained prominence in 2022 with a series of high-profile data leaks, first making headlines in March by exposing over 105 million Indonesian voter records. Throughout 2022, Bjorka targeted multiple institutions, leaking personal data to highlight security flaws and criticize policies. By August 2022, Bjorka joined BreachForums, where they are sharing large databases from breached telecom services. Authorities attempted to identify the hacker, even arresting an individual, but Bjorka mocked the effort, claiming the wrong person was caught. The threat actor is active on BreachForums and Telegram and owns a personal leak site (netleaks[.]net) to distribute stolen data and engage followers.
Figure 4 – The Telegram user of Bjorka
Babuk Locker 2.0/Babuk-Bjorka
Since February 2025, Skywave has claimed ownership on at least 5 different Telegram channels and posts daily about their previous and current victims. Throughout the research, we found dozens of newly created Telegram channels with the names ‘Babuk Locker 2.0’, ‘Babuk 2.0 Ransomware Affiliates’, etc. Some of which overlapped with one another. Additionally, several channels were labeled as scams by Telegram itself and were unavailable a couple of days after they were created.
Figure 5 – A Babuk Locker Telegram channel labeled as a scam by the platform
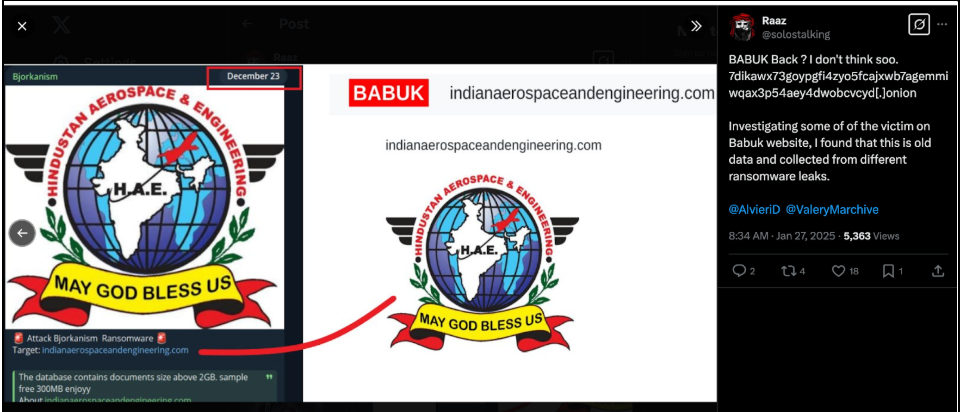
During our research, we noticed the consistent amplification of the Babuk 2.0 content by Bjorka on their Telegram channel. Speculation about the possible affiliation between Babuk and Bjorka rose due to the overlap of victims, such as the case of ‘Hindustan Aerospace & Engineering’ from India. The organization was initially reported as a victim of Bjorka in December 2023, and again as a victim of Babuk as of March 2025.
Figure 6 – Overlap of victimology between Bjorka and Babuk 2.0
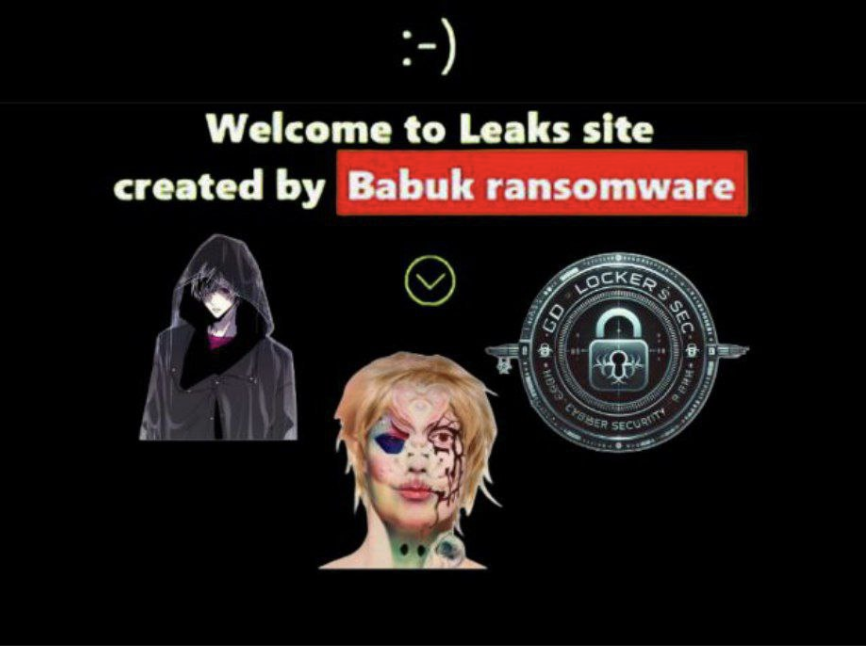
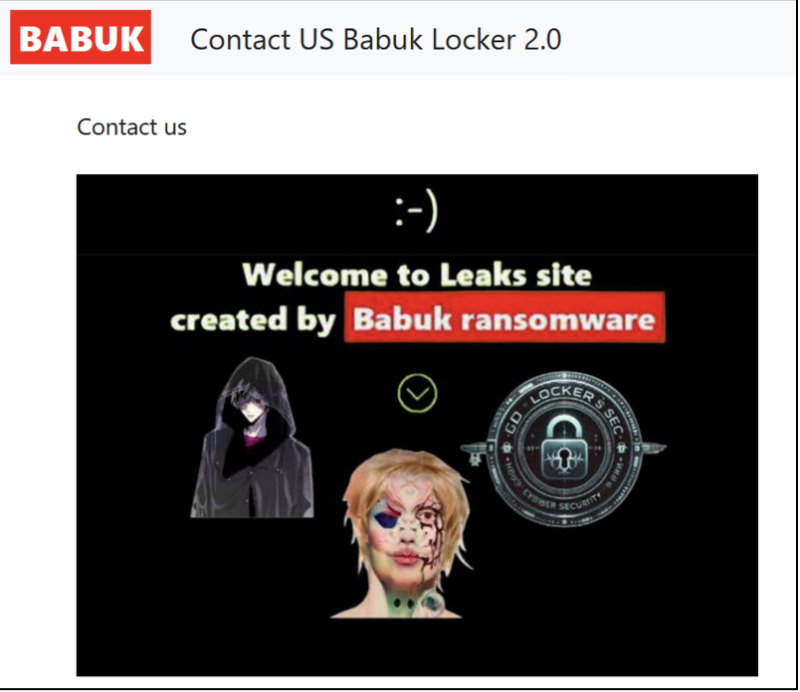
Further evidence of a possible collaboration between the threat actors emerges from the ‘Contact Us’ tab on Babuk’s DLS, where the logos of Skywave and Bjorka appear next to each other, as well as another possible affiliate named GD Locker Sec.
Figure 7 – The ‘Contact US’ tab on the DLS of Babuk, showing the logos of Bjorka and Skywave
Technical Analysis
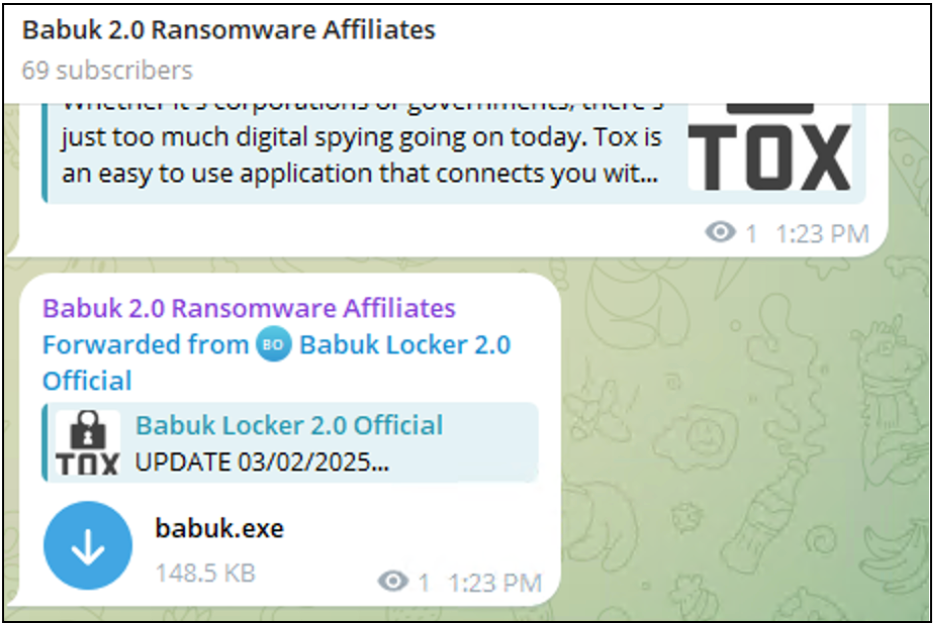
A sample named babuk.exe SHA-256 3facc153ed82a72695ee2718084db91f85e2560407899e1c7f6938fd4ea011e9 was initially shared on the Telegram channel “Babuk 2.0 Ransomware Affiliates”, before being forwarded to another operational account. Upon analysis, it turned out not to be Babuk Locker at all, but rather LockBit 3.0 also known as LockBit Black. This case is yet another example of the well-established trend: threat actors rebranding ransomware strains, whether to confuse researchers, lure affiliates, or just keep the marketing fresh. Either way, babuk.exe is just LockBit 3.0/Black wearing a fake name.
Figure 8 – “Babuk” sample shared on Babuk 2.0 Affiliate Group Telegram channel
LockBit 3.0 Overview
LockBit 3.0/Black, is a ransomware variant that shares similarities with BlackMatter ransomware. On September 21, 2022, a user named @ali_qushji leaked the LockBit 3.0 builder on Twitter. The leak code made it easy for the least skilled attackers to join the game.
Encryption Methods
An analyzed sample of LockBit 3.0 uses a combination of AES-256 and RSA-2048 encryption. AES-256 is used to encrypt victim files and RSA-2048 encryption used to encrypt the AES key, ensuring decryption is impossible without the attacker’s private key.
Terminated Processes and services
LockBit 3.0 terminates various applications and system processes (the full list is in the table below) most likely to maximize encryption efficiency and prevent file access conflicts. It also disables key security and backup services to limit recovery possibilities and increase impact.
Terminated Processes
Terminated Services
sql
vss
oracle
sql
ocssd
svc
dbsnmp
memtas
synctime
mepocs
agntsvc
msexchange
isqlplussvc
sophos
xfssvccon
veeam
mydesktopservice
backup
ocautoupds
GxVss
encsvc
GxBlr
firefox
GxFWD
tbirdconfig
GxCVD
mydesktopqos
GxCIMgr
ocomm
dbeng50
sqbcoreservice
excel
infopath
msaccess
mspu
onenote
outlook
powerpnt
steam
thebat
thunderbird
visio
winword
wordpad
notepad
calc
wuauclt
onedrive
Active Directory Enumeration
LockBit 3.0 uses logoncli_DsGetDcNameW API function used for Active Directory (AD) enumeration. To brute-force AD accounts, analyzed LockBit 3.0 sample came preloaded with Base64-encoded username and password combinations decoded and listed below.
Username
Password
bad.lab
Qwerty
Administrator
123QWEqwe
@#Admin2
P@ssw0rd
Administrator
P@ssw0rd
Administrator
Qwerty
Administrator
123QWEqwe
Administrator
123QWEqweqwe
Babuk or LockBit 3.0? Rebranding Won’t Change the Code.
Analysis confirms that babuk.exe, advertised in the Babuk 2.0 Ransomware Affiliates Telegram channel, is actually based entirely on LockBit 3.0 source code—not Babuk. The sample shows key techniques identical to previous LockBit 3.0 variants, reinforcing that this is yet another case of threat actors rebranding existing ransomware rather than introducing anything genuinely new.
Key Overlapping Techniques
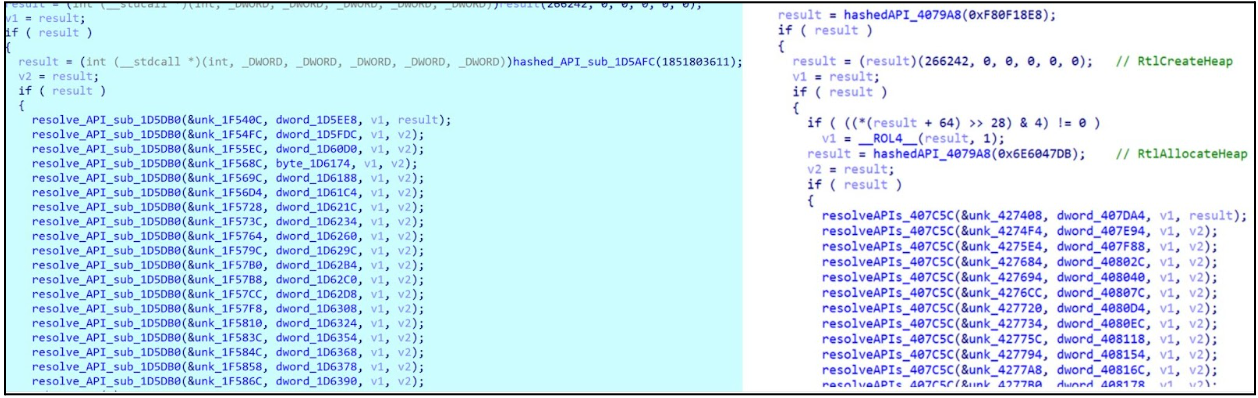
The analyzed sample uses API harvesting by hashing API names from DLLs and comparing them against a predefined list of required APIs (Figure 7). This technique, likely to obfuscate API calls and evade detection, mirrors the approach seen in Lockbit3.0/Black and aligns with previous findings by Trend Micro.
Figure 9 – LockBit 3.0’s routine for API harvesting function comparison—our analyzed sample (left) vs. TrendMicro’s reported sample (right).
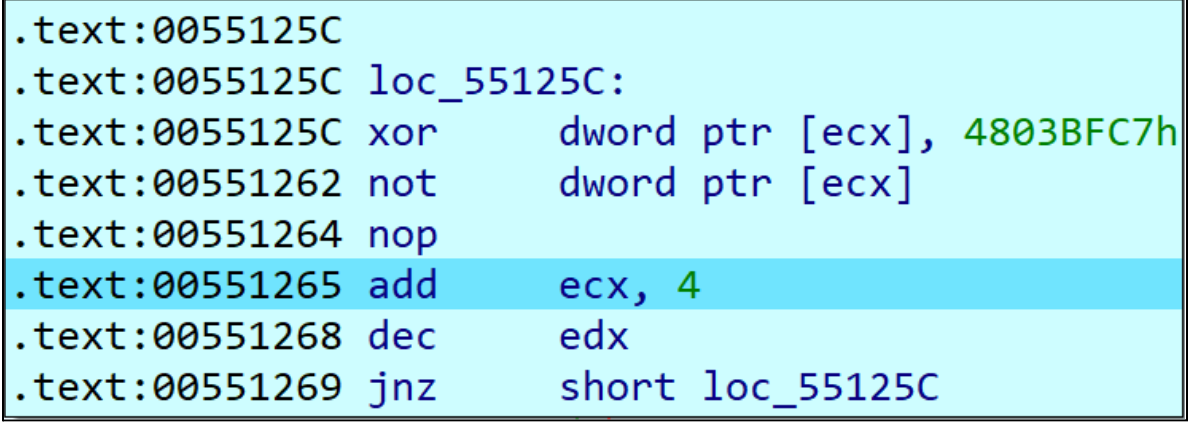
Likewise, The XOR key 0x4803BFC7 LockBit 3.0 used for renaming APIs is the same as it was reported before. The xor key is re-used multiple times in the code.
Figure 10 – 0x4803BFC7 xor key observed in analyzed sample
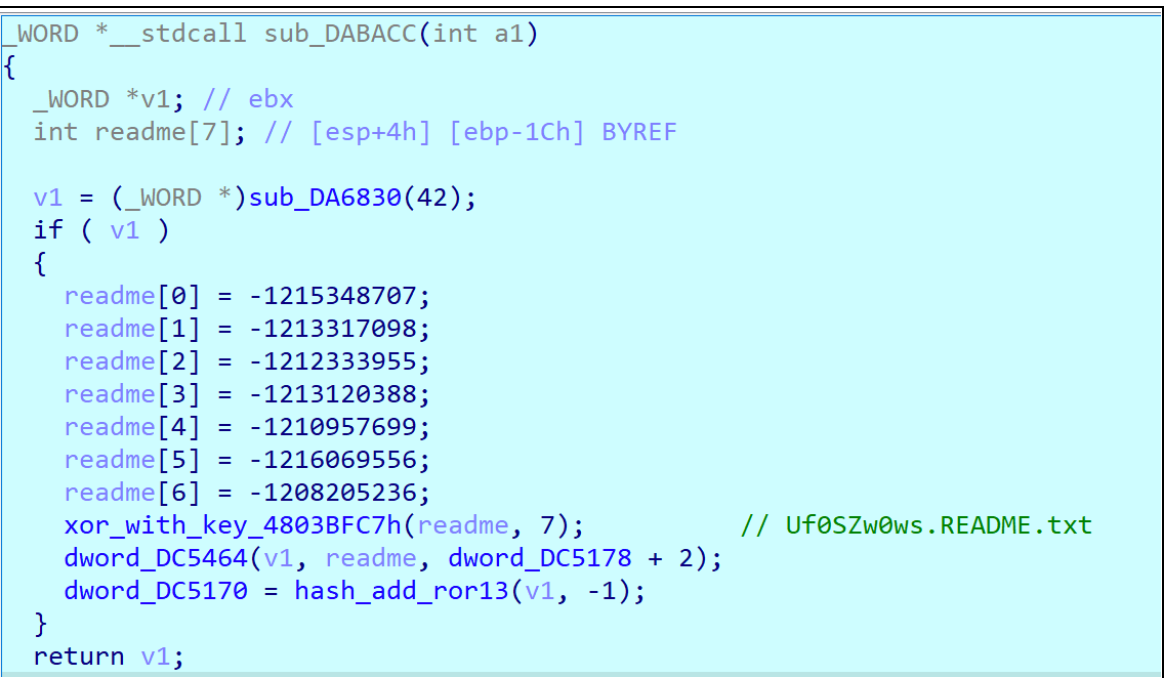
Additionally, the ransom note creating routine is identical as in previous Lockbit3.0/Black samples.
Figure 11 – readme creation routine
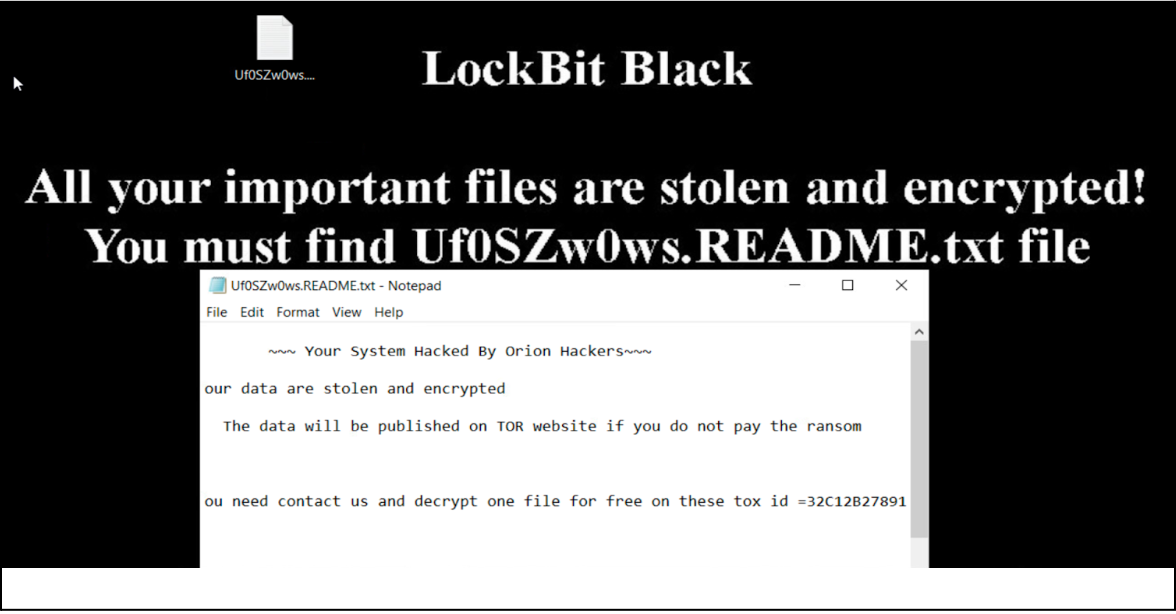
Like previous LockBit 3.0/ Black samples, the analyzed variant modifies the desktop wallpaper to display a ransom note—branded, unsurprisingly, as “LockBit Black” (not Babuk, in case anyone was still confused). It also appends specific extensions to encrypted files, changes their icons, and drops a .ico file in the %PROGRAMDATA% directory, staying true to the LockBit playbook.
Figure 12 – Lockbit3.0 wallpaper and ransom note
The ransom note referenced “Orion Hackers” and the tox ID 32C12B278912E26E5EAC57AEBB3F4FF16F0E31603C7B9D46AC02E9D993EE14351CEC3AB5945C. A search on this TOX ID linked the ransom demands to the `Babuk 2.0 Affiliate Group` on Telegram. Additionally, we discovered that messages from this channel were being reposted by an actor named Bjorkanism, who is actively sharing content from Affiliate Group Babuk 2.0 which is actually leaked Lockbit3.0.
Victimology
The new Babuk Locker 2.0 has recently been making waves within the cybersecurity and intelligence scene, claiming dozens of high-profile cyberattacks in a short time of less than two months of operation. Since January 2025, the group has listed at least 100 organizations as their alleged victims. Among their alleged victims are Amazon, the Israeli Knesset, Sodexo, and other high-profile organizations. Victims are from multiple sectors including energy, manufacturing, IT, government, etc.
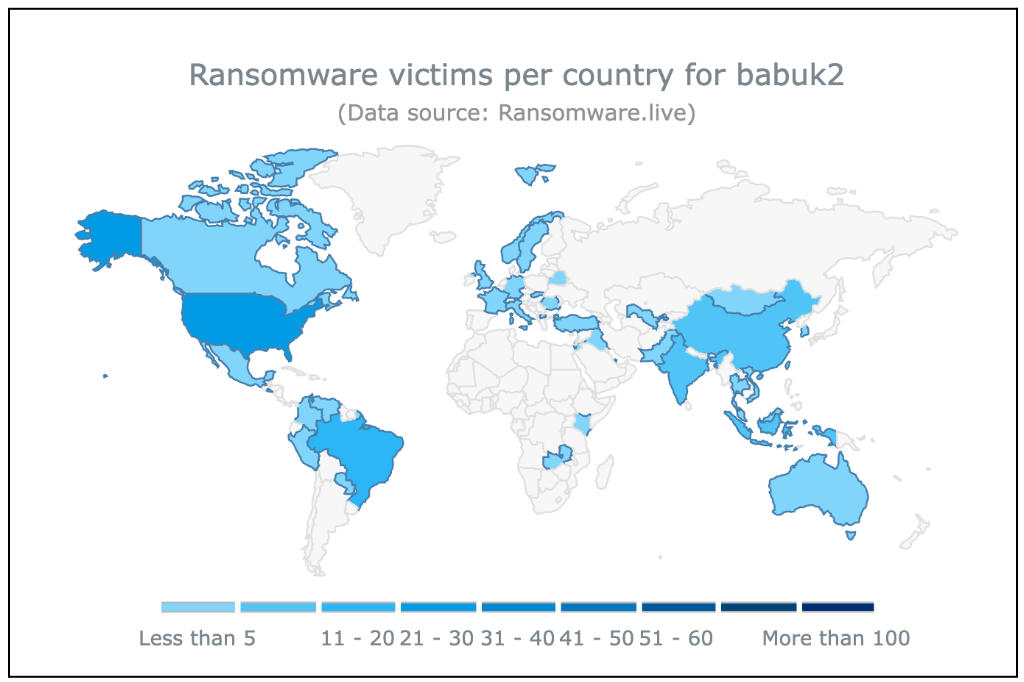
Figure 13 – Victims listed on the Babuk Locker 2.0 DLSFigure 14 – Babuk Locker 2.0 victims per country
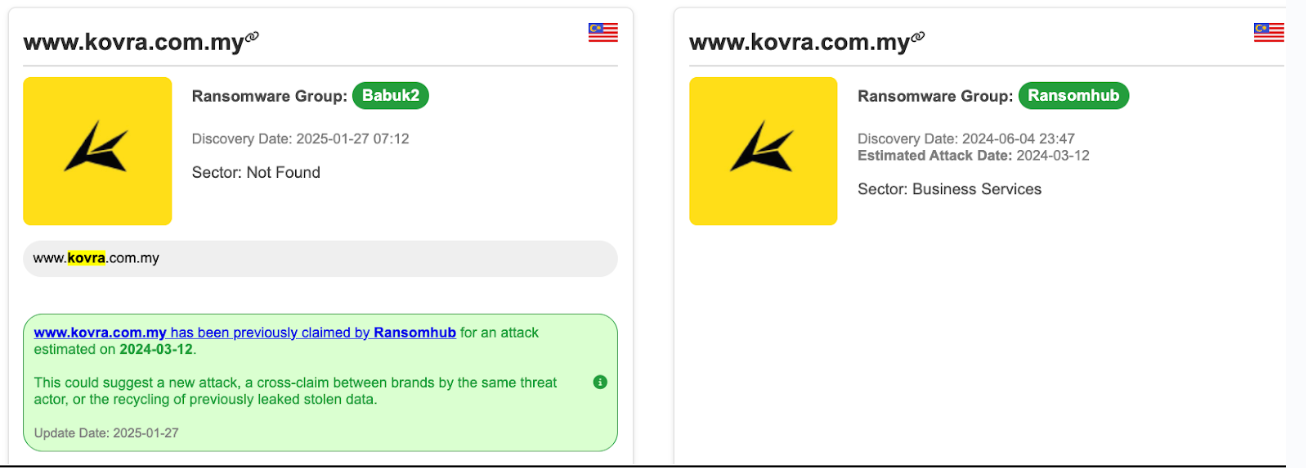
There have been growing claims of overlaps between Babuk Locker 2.0 and other ransomware groups, as some of their alleged victims were already attacked by other groups, such as HellCat, RansomHub, FunkSec, and others. These overlaps in victimology reinforce concerns about the authenticity of the new Babuk group entity and its operations.
Figure 15 – Babuk Locker 2.0 victims overlap with another ransomware group
Conclusion
Babuk Locker 2.0 is not a true revival of the original Babuk group—it’s just LockBit 3.0 with a new label. Our analysis strongly suggests that Skywave and Bjorka are behind this operation, either as collaborators or opportunistic actors riding the same wave.
Despite its bold claims, Babuk 2.0’s victim list overlaps heavily with other ransomware groups, raising doubts about the legitimacy of its attacks. Rather than a sophisticated new threat, this looks more like a rebranding stunt—a common tactic among ransomware operators to confuse defenders, attract affiliates, and inflate their reputation.
This case reinforces a familiar pattern: ransomware groups don’t disappear—they just change names, recycle code, and keep cashing in. Whether Skywave and Bjorka are working together or simply using Babuk’s name for credibility, one thing is clear: Babuk 2.0 is just LockBit 3.0 in a different costume.
The following is a guest blog post by Zac Youtz, Co-Founder and CTO at valued Rapid7 partner, Furl. Here, Zac discusses how to effectively remediate vulnerabilities discovered by Rapid7’s InsightVM.
Scaling vulnerability remediation with AI
Vulnerability remediation is a crucial-yet-complex task for organizations striving to maintain a strong security posture. Security teams work tirelessly to identify and prioritize vulnerabilities, often based on severity. However, true remediation remains a challenge due to the involvement of multiple stakeholders, the limitations of traditional tools, and the lack of flexibility in addressing vulnerabilities effectively.
The complexity of multi-stakeholder remediation
While security teams are responsible for identifying and prioritizing risks, they may not always have full visibility into the broader business context or IT infrastructure. IT teams, on the other hand, must evaluate the potential business impact of each vulnerability and determine the most effective remediation strategy.
This decentralized approach often requires collaboration across multiple departments, including system administrators, application owners, and other technical teams. The result is a remediation process that can become fragmented, delayed, and hindered by misalignment in priorities and resource constraints.
The gap between tools and remediation needs
Traditional endpoint and patch management tools are not designed to fully address the nuances of vulnerability remediation. While they serve a critical role in maintaining system integrity and enforcing security policies, they often lack the adaptability required for addressing the evolving nature of security threats. Some of the key challenges include:
Limited context awareness: Patches are applied without considering the broader business or technical impact, which can lead to system disruptions.
Rigid approaches: A one-size-fits-all methodology fails to account for varying vulnerability severities and business risks, delaying critical fixes.
Limited remediation flexibility: Most endpoint management and patching tools only manage software within their scope, leaving gaps for software installed outside IT control—resulting in unmanaged vulnerabilities that are often ignored or addressed through a growing list of exceptions.
Limited remediation approaches: Patching isn’t always the only or best fix. Uninstalling unused or unnecessary software can eliminate risk entirely, but many tools lack the visibility to support this approach.
Poor coordination: Limited alignment between security, IT, and application teams can slow down remediation efforts.
Inflexible policies: Static policies struggle to adapt to the dynamic nature of emerging threats and evolving infrastructure.
To bridge these gaps, organizations need a more intelligent and context-aware approach that enhances traditional remediation tools rather than replacing them.
Enhancing InsightVM with AI-powered remediation
Rapid7’s InsightVMis designed to help organizations manage and respond to potential threats quickly and effectively. Furl’s AI-powered platformcan be an accelerator of efficient remediation of those threats by integrating with InsightVM. This partnership enables organizations to take immediate and automated action on vulnerabilities identified through Rapid7’s threat intelligence. Furl’s AI-driven remediation engine can:
Automate fixes: Instantly apply the most effective remediation strategies tailored to the vulnerability type and business impact.
Improve coordination: Bridge the gap between managed detection and response (MDR) findings and IT teams, ensuring vulnerabilities are addressed without unnecessary delays.
Enhance contextual decision-making: Provide enriched insights that help prioritize and execute remediation steps in line with MDR recommendations.
Streamline workflows: Reduce the burden on security teams by seamlessly integrating with existing security operations processes and toolsets.
Partnering for an efficient remediation strategy
To help organizations tackle these challenges, Rapid7 is partnering with innovative security solutions like Furl, a company dedicated to transforming the remediation process with AI-driven automation. Through this collaboration, Rapid7 InsightVM customers can benefit from automated, intelligent remediation workflows that accelerate response times and improve overall security outcomes.
By combining Rapid7’s industry-leading detection and response capabilities with Furl’s AI-powered remediation platform, organizations can move from identification to resolution faster—closing the loop on vulnerability management and ensuring threats are neutralized before they can cause harm.
Rapid7 has been honored by CRN®, a brand of The Channel Company, with a 5-Star Award in the 2025 CRN Partner Program Guide. This annual guide is an essential resource for solution providers seeking vendor partner programs that match their business goals and deliver high partner value.
Recognition of Rapid7’s continued commitment to channel
The 5-Star Award is an elite recognition given to companies that have built their partner programs on the key elements needed to nurture lasting, profitable, and successful channel partnerships
When evaluating potential collaborations with IT vendors, Partners must carefully consider the comprehensive support and resources offered through vendors’ partner programs. Key program components, including financial incentives, sales and marketing support, training and certification, and technical assistance – can significantly distinguish vendors such as Rapid7. These elements are instrumental in enhancing the long-term growth and profitability of their partnerships.
For the 2025 Partner Program Guide, the CRN research team evaluated vendors based on program requirements and offerings such as partner training and education, pre- and post-sales support, marketing programs and resources, technical support, and communication. Rapid7 acknowledges the significance of these critical program features and is pleased to have integrated all of these elements into the 2025 PACT program.
Aligned with our recent program launch
This prestigious recognition closely follows the introduction of the enhanced 2025 PACT Partner Program. Rapid7 recognizes that in today’s increasingly complex threat landscape, partners face mounting pressure to have access to the tools, training, and resources necessary to meet the expanding security demands of their clients. Rapid7 is strategically positioned to fulfill these essential partner needs, having launched the revitalized Partner Program PACT 2025. This comprehensive program is designed to represent and support our expanding community of partners – encompassing diverse business models – all unified under a cohesive framework with competitive benefits and partnership support.
Being featured in the 2025 CRN Partner Program Guide highlights the dedication these technology vendors have to evolving with solution providers, driving innovation, and supporting mutual success,” said Jennifer Follett, VP, U.S. Content and Executive Editor, CRN, at The Channel Company. “This critical annual project empowers solution providers to identify vendors that are committed to enhancing their partner programs and meeting the always-changing business needs of the channel and end customers. The guide provides deep insight into the distinctive value of each partner program so solution providers can make strategic partnership decisions with confidence.”
Future outlook: Sustained focus and commitment
Our dedication to our partners is unwavering, as we continue to engage collaboratively with our global partner network. We are committed to understanding the needs of our partners as well as addressing business challenges and opportunities.
We will continue to develop strategies that improve the ease and efficiency of our business engagements, ensuring exceptional experiences and exemplifying our partner-first culture. Our programs are developed in collaboration with our partners, and maintaining a continuous feedback loop is essential as we work to evolve and enhance our offerings.
With Take Command 2025 just around the corner, we sat down with Raj Samani, Chief Scientist at Rapid7, for a preview of his upcoming session: Inside the Mind of an Attacker: Navigating the Threat Horizon.
Raj will be joined by Trent Teyema, Founder and President at CSG Strategies and former head of the FBI Cyber Division, and moderator Brian Honan, CEO of BH Consulting. Together, they bring decades of experience across cyber intelligence, national security, and frontline incident response.
So what can attendees expect from the session, and the day as a whole?
A Panel Built for Practical Impact
“This isn’t a talking shop,” Raj told us. “The people on this panel are practitioners. They do the job.”
Rather than focus on theory, the session aims to provide clear, actionable guidance rooted in real-world expertise. Raj describes the panel as a rare convergence of perspectives: vendors developing the tools, consultants advising organizations directly, and former government leaders who’ve pursued and prosecuted threat actors.
“We’ve got three legs of the solution represented,” he said. “And the audience is the fourth. Between us, we’re covering every side of the response equation.”
The Shift in Attacker Capabilities
While Raj didn’t give away too much ahead of the session, he offered a clear warning: attacker capabilities have evolved—rapidly.
“In the past, tools and techniques used by advanced nation-state actors were out of reach for most criminals,” he explained. “Now, even relatively inexperienced threat actors have access to those same capabilities. That changes everything.”
Organizations today face a constant flood of vulnerabilities, alerts, and data to prioritize – often without the context needed to make effective decisions.
“It’s not that we have a data problem,” Raj noted. “It’s that we have a context problem. We’re overwhelmed, and the inability to act quickly and decisively is putting organizations at risk.”
That’s where visibility and prioritization come into play—two capabilities central to Exposure Management and solutions like Rapid7’s Exposure Command.
Why This Session Matters
Raj emphasized that this session is about helping practitioners walk away with tangible answers to critical questions:
How do I know if I’ve been compromised?
Are adversaries still in my network?
Which vulnerabilities actually matter?
What can I do to reduce risk—today?
“These are the questions every security leader needs to be able to answer. Because if you can’t, how long will your executive team trust you to lead the charge?”
Why Attend Take Command 2025?
Raj was clear: this isn’t just another virtual event.
“Take Command is one of our most important moments of the year,” he told us. “It’s where we bring everything together, sharing the latest research, strategies, experiences and innovations from those on the front lines.and give people the chance to hear what’s actually happening on the front lines.”
He also noted that sessions like his don’t come around often, making this a rare opportunity to hear directly from experts working across national security, threat intelligence, and hands-on incident response.
Don’t Miss It
Take Command 2025 takes place April 9, 2025, and features a full day of virtual sessions covering AI, MDR, threat intelligence, red teaming, and more.
Raj Samani’s panel, “Inside the Mind of an Attacker,” is one you won’t want to miss.
AWS GuardDuty has introduced two powerful new alerts that enhance its threat detection capabilities: “Potential Credential Compromise” and “Potential S3 Data Compromise.” These alerts go beyond traditional threat detection by focusing on attack sequences, providing deeper insights into suspicious activities that may indicate credential misuse or unauthorized data access.
Unlike single-event alerts, these new notifications correlate multiple signals across different timeframes and contexts, helping organizations detect sophisticated attack strategies such as persistence, privilege escalation, and data exfiltration. These advanced alerts represent a significant shift in cloud security, enabling users to take faster, more informed actions against potential threats.
Rapid7’s Managed Threat Complete supports third party cloud security tools, includingAWS GuardDuty alerts, by providing critical capabilities such as alert triage, remediation recommendations, and response actions, helping SOC analysts reduce response time and improve operational efficiency for customers. The Rapid7 SOC has increased their coverage for these new AWS alerts, let’s take a look at each of them and how they work.
AttackSequence:IAM/CompromisedCredentials – Detecting IAM Credential Abuse
The IAM Compromised Credentials alert identifies potential credential theft and abuse within AWS environments by correlating multiple suspicious activities, such as:
Connection attempts from known malicious IP addresses (e.g., Tor exit nodes)
High-risk API calls, including attempts to disable security controls
Actions aligning with multiple MITRE ATT&CK tactics and techniques
Suspicious privilege escalation attempts
This alert tracks the progression of an attack from initial access attempts to defense evasion techniques like CloudTrail deletions. It provides detailed information about the affected IAM entities, specific API calls made, and geographic origins of suspicious connections, enabling security teams to assess and respond rapidly to potential threats.
AttackSequence:S3/CompromisedData – Protecting Your S3 Data
The S3 Compromised Data alert focuses on detecting potential data breach attempts targeting S3 buckets. This detection mechanism monitors for activity sequences that indicate an attacker attempting to locate, access, or exfiltrate sensitive data. Key aspects of this alert include:
Identification of suspicious S3 bucket enumeration activities
Detection of unusual data access patterns
Monitoring of security control modifications
Tracking of potential data exfiltration attempts
By correlating various activities such as ListBuckets, GetObject, and DeleteObject operations—especially when performed from suspicious IP addresses or in conjunction with bucket access modifications—this alert helps security teams identify and respond to potential data breaches before significant damage occurs.
Both of these new alert types represent a major advancement in AWS security monitoring, providing teams with more context-aware and actionable insights. Implementing these alerts allows organizations to better protect their AWS environments from sophisticated attack sequences and potential data breaches.
Rapid7 Managed SOC Powered by CDR & ICS
Rapid7’s expert-driven cloud-ready MDR solution offers 24/7 monitoring and continuous tracking and response to cloud threats in real-time. Rapid7 Exposure Command automatically enriches alerts from third-party detection engines, such as AWS GuardDuty and Azure Microsoft Defender for Cloud, to accelerate SOC investigation and response, ensuring threats are contextualized effectively.
With a proactive approach, Rapid7 SOC analysts manage critical incidents to minimize risk and enhance cloud security by reducing response time through enriched insights provided by ICS. InsightCloudSec delivers comprehensive cloud security, helping organizations:
Stay compliant by enforcing security policies and addressing security gaps
Reduce attack surface by identifying and fixing risky IAM roles, misconfigurations, and unused resources
Eliminate risks by identifying issues early to minimize vulnerabilities and strengthen the cloud environment
Contact us to learn more about how Managed Threat Complete and InsightCloudSec brings enhanced cloud detection and response to help customers command their attack surface.
On Wednesday, March 19, 2025, backup and recovery software provider Veeam published a security advisory for a critical remote code execution vulnerability tracked as CVE-2025-23120. The vulnerability affects Backup & Replication systems that are domain joined. Veeam explicitly mentions that domain-joined backup servers are against security and compliance best practices, but in reality, we believe this is likely to be a relatively common configuration.
Veeam’s advisory indicates that the vulnerability is authenticated, though the CVSS score for CVE-2025-23120 is listed as 9.9. The advisory itself states that “authenticated domain users” can exploit the vulnerability but says little else — it’s possible that additional exploitation criteria will be published later on. According to Veeam, all supported versions of Backup & Replication are affected.
No public proof-of-concept exploit has been released (at time of this blog’s publication). Veeam Backup & Replication has a very large deployment footprint, and backup solutions are commonly targeted by threat actors. Veeam Backup & Replication should not be exposed to the internet and makes for a more effective internal attack vector than an external vector. Still, plenty of previous Veeam Backup & Replication vulnerabilities have been exploited in the wild, including by ransomware groups.
As we have mentioned previously, more than 20% of Rapid7 incident response cases in 2024 involved Veeam being accessed or exploited in some manner, typically once an adversary has already established a foothold in the target environment.
Mitigation guidance
Veeam Backup & Replication 12.3.0.310 and all earlier version 12 builds are vulnerable to CVE-2025-23120, per the vendor advisory.
Customers should update to the latest version of the software (12.3 build 12.3.1.1139) immediately, without waiting for a regular patch cycle to occur. Per the vendor, unsupported software versions were not tested but should be considered vulnerable.
Rapid7 customers
InsightVM and Nexpose customers will be able to assess their exposure to CVE-2025-23120 with a vulnerability check expected to be available in tomorrow’s (Thursday, March 20) content release.
Take Command 2025 is bringing together some of the sharpest minds in cybersecurity to tackle today’s most urgent challenges. From attacker methodologies and AI-driven security to MDR, red teaming, and exposure management, this year’s virtual event will provide security professionals with practical insights, cutting-edge research, and real-world defense strategies.
While we’ve already announced an impressive lineup of industry experts, we’re excited to introduce even more voices joining the discussion. These new speakers will bring fresh perspectives and invaluable expertise to the Take Command 2025 stage, making this year’s event even more essential for security practitioners, team leaders, and researchers.
Shawnee Delaney: Cyber Intelligence, Insider Threats & AI Resilience
Cyber threats aren’t just external—insider risks, intelligence tactics, and machine-driven attacks are playing an increasingly significant role in security breaches. Shawnee Delaney, CEO of Vaillance Group and expert on cybersecurity, insider threat & counterintelligence, brings deep expertise in intelligence-driven security, insider threat management, and proactive cyber defense strategies.
Her session, ‘Rise of the Machines: Building Cyber Resilience with AI’, will explore:
How organizations can manage overwhelming volumes of security data using big data analytics, data fabric, and Generative AI
Strategies for leveraging AI-driven insights to detect and mitigate emerging threats
The balance between automation, human expertise, and proactive risk management in modern security operations
This session will provide practical, real-world takeaways for security teams looking to harness AI effectively in their operations.
Future-Proofing Vulnerability Management with Rapid7 customers
Security teams are shifting from traditional vulnerability scanning to proactive exposure management, and leading organizations are pioneering new strategies. In this panel, security leaders from Miltenyi Biotec , Phibro Animal Health Corporation, and Cross Financial Corp.will share firsthand insights on how they are evolving their vulnerability management programs to keep pace with today’s complex threat landscape.
Moderated by Aniket Menon, VP, Product Management at Rapid7, this session, Expert Tips to Help You Future-proof Your VM Program with Continuous Attack Surface Visibility, will explore real-world experiences from security leaders implementing modern vulnerability management frameworks. They will discuss the challenges of adapting to emerging threats, lessons learned from refining their security programs, and best practices for improving visibility and risk prioritization. This customer-led discussion will provide actionable insights for security teams looking to strengthen their exposure management strategies and build a more resilient security posture.
Industry Experts Leading the Conversation
Take Command 2025 brings together top cybersecurity minds to explore threat intelligence, AI-driven security, exposure management, and evolving regulations. Raj Samani (Rapid7) and Trent Teyema (CSG Strategies, former FBI Special Agent) will break down attacker methodologies, while Will Hunt (In.Security) will discuss how red teaming is adapting to modern threats.
Ted Harrington (ISE) and Tyler Shields (ESG) will share strategies on AI-driven defense and proactive risk management, while Sabeen Malik (Rapid7) will guide CISOs through pieces of legislation that are considered important for cybersecurity.. Throughout the event, Rapid7’s SOC and MDR experts will offer real-world insights into evolving detection and response strategies.
The Tempest Two: Lessons in Resilience
Cybersecurity isn’t just about technology—it’s about mindset, resilience, and adaptability. The Tempest Two will bring a unique perspective on overcoming challenges and decision-making under pressure, drawing from their experiences tackling some of the world’s most extreme endurance challenges.
Their session will provide actionable takeaways on mental resilience and adaptability, offering insights that security professionals can apply to cyber incident response, crisis management, and high-pressure decision-making.
Register Now to Take Command 2025
Take Command 2025 is a free, global, virtual event happening on April 9. Don’t miss your chance to hear from security leaders and experts on the biggest challenges shaping the industry.
What is Continuous Threat Exposure Management (CTEM)?
Continuous Threat Exposure Management (CTEM) is a five-stage, continuous security program introduced by Gartner in 2022. It proactively assesses an organization’s exposure across networks, systems, cloud infrastructure, IoT devices, applications, and identities. Unlike traditional vulnerability assessments, CTEM prioritizes risk mitigation strategies and iteratively refines security postures through continuous validation and remediation.
By emphasizing offensive security techniques such as continuous red teaming and simulation-based testing, CTEM goes beyond basic vulnerability prioritization to identify and address weaknesses before adversaries can exploit them. The result is an adaptable, intelligence-driven security framework that enables organizations to transition from reactive defenses to proactive resilience.
Why Should Service Providers Care?
The MSSP market is increasingly competitive, and differentiation is critical. Gartner has identified CTEM as a key opportunity for MSSPs in 2024, emphasizing that “product leaders who differentiate their portfolios by offering services that result in prioritized remediation outcomes and measured reduction in exposure stand out in the crowded MSSP market.”
Moreover, the expansion of the attack surface – combined with the inability to patch all vulnerabilities in a timely manner -has made traditional vulnerability management insufficient. MSSPs must demonstrate how their services deliver tangible security benefits to customers. A well-structured CTEM program enables MSSPs to provide a continuous, data-driven security validation framework that reduces risk while aligning stakeholders across IT, security, and leadership teams.
CTEM: A Programmatic Approach
Unlike traditional security programs that rely on static tools, CTEM is an adaptive program that integrates offensive security methodologies, including red teaming, penetration testing, vulnerability management, cloud security posture management, and web application security. This holistic approach ensures alignment with Governance, Risk, and Compliance (GRC) initiatives while delivering continuous security improvements.
The Five Stages of a CTEM Program
1. Scoping: Defining the Attack Surface
Scoping, as defined by Gartner, involves identifying an organization’s complete attack surface. This is where Surface Command, a key component of the Exposure Command suite, provides critical visibility by combining Cyber Asset Attack Surface Management (CAASM) with External Attack Surface Management (EASM). Unlike point-in-time assessments, Surface Command offers continuous monitoring of assets across on-prem, cloud, and SaaS environments, ensuring that no shadow IT or misconfigured exposure goes undetected.
2. Discovery: Mapping Assets, Vulnerabilities, and Risks
Discovery involves identifying both known and hidden assets, vulnerabilities, and misconfigurations. A common pitfall is confusing scoping with discovery—simply identifying a large number of vulnerabilities does not equate to security success.
Rapid7 Exposure Command enhances the discovery phase by integrating InsightVM for vulnerability management, InsightAppSec for dynamic application security testing (DAST), and InsightCloudSec for cloud security posture management (CSPM). These tools work together to provide comprehensive visibility intoexposure across hybrid environments.
3. Prioritization: Focusing on What Matters
Not all security issues require immediate remediation. Effective prioritization should factor in:
Business risk and potential impact
Urgency and exploitability
Availability of compensating controls
Tolerance for residual attack surface
Rapid7 Exposure Command’s risk-based prioritization framework goes beyond CVSS scoring by incorporating real-world exploitability data, asset criticality, and threat intelligence. The Command Platform provides a unified view of risks and remediation priorities, enabling MSSPs to help customers focus on the most impactful security improvements.
4. Validation: Proving Security Effectiveness
Validation is the cornerstone of CTEM. Organizations must confirm that vulnerabilities are exploitable, understand potential attack paths, and assess the effectiveness of security controls.
MSSPs can use continuous red teaming, penetration testing, and adversary simulations to validate security postures. Additionally, Security Information and Event Management (SIEM) solutions provide real-time threat correlation, ensuring organizations can detect and respond to threats before they escalate.
The final stage of CTEM is mobilizing findings into actionable security improvements. This involves:
Streamlining approval workflows for remediation
Automating patch management and configuration changes
Ensuring alignment between IT, security, and executive teams
Rapid7 Exposure Command facilitates mobilization by providing automation and orchestration capabilities, reducing friction in vulnerability remediation processes. By integrating with existing IT workflows, MSSPs can ensure that security enhancements are implemented efficiently and effectively.
Achieving a Secure Environment with CTEM
The burden of threat management continues to grow as attack surfaces expand and adversaries evolve. MSSPs must help organizations move beyond traditional vulnerability management to a continuous, risk-driven security approach.
By leveraging ExposureCommand, MSSPs can:
Provide continuous visibility into evolving threats and vulnerabilities
Enable proactive risk mitigation through prioritized remediation
Validate security effectiveness through ongoing testing and adversary simulations
Streamline remediation efforts with automation and orchestration
CTEM is not just a security strategy—it’s a key differentiator for MSSPs. By embedding CTEM into their service offerings, MSSPs can deliver measurable risk reduction, enhance customer trust, and solidify their role as strategic security partners.
The cybersecurity landscape is shifting fast—ransomware is evolving, AI is reshaping security operations, and regulations are becoming more complex than ever. Security teams are under pressure to outpace adversaries, manage risk, and defend against sophisticated threats.
That’s why Take Command 2025 is built to deliver the most relevant, actionable insights security leaders need to navigate these challenges. This full-day virtual event brings together top security minds—from Rapid7’s experts to industry analysts and frontline defenders—covering the strategies, tools, and intelligence to help you take command of your attack surface.
A pre-recorded message from Rapid7 CEO Corey Thomas is already live on our event site, providing an inside look at what you can expect from Take Command 2025, and how our global summit will help security teams stay ahead of emerging threats.See the full list of speakers and watch Corey Thomas’s message on the Take Command 2025 registration page.
A Glimpse Into This Year’s Key Themes
This year’s agenda is packed with deep-dive discussions, real-world case studies, and expert insights on the most pressing security topics today. Here are just a few of the key focus areas you can expect at Take Command 2025:
Understanding the Evolving Threat Landscape
Cybercriminals are always one step ahead—until you learn to think like they do. This panel discussion, led by Raj Samani, Rapid7’s Chief Scientist, will explore the latest attack methodologies, emerging ransomware tactics, and evolving adversary behaviors.
Raj will be joined by Trent Teyema, Founder and President of CSG Strategies, a former FBI Special Agent (SES retired), as they analyze real-world attacker techniques and share how security teams can leverage threat intelligence to anticipate and disrupt threats before they escalate.
Session: Inside the Mind of an Attacker: Navigating the Threat Horizon
AI & Cloud Security: Opportunities and Challenges
AI is transforming cybersecurity, but how can organizations implement it responsibly and effectively? Take Command 2025 will examine:
The future of AI-powered security operations—what’s hype vs. reality?
How SOC and MDR teams are leveraging AI to improve detection and response
Cloud security challenges and why cloud detection & response (CDR) is becoming a critical SOC capability
Thom Langford, Regional CTO at Rapid7, will host this discussion, featuring Ted Harrington, Executive Partner at ISE (the Company of Ethical Hackers). Together, they will explore how AI-powered, Zero Trust-based security models are changing how organizations approach risk and resilience, and what the next era of cybersecurity defense will look like in our ‘From Zero to Hero: Building the Perfect Defense’ session.
Exposure Management & Red Teaming: Proactive Security in Action
Security teams can’t afford to wait for attacks to happen. Implementing proactive security strategies are critical. Take Command 2025 will explore:
How red teaming is evolving to match today’s complex threat landscape
Real-world lessons from leading vulnerability management programs
Why organizations are shifting from traditional vulnerability scanning to proactive exposure management
Industry analyst Tyler Shields (ESG) and offensive security consultant Will Hunt (In.Security) will lead key discussions, sharing practical insights on prioritizing risk, testing defenses, and staying ahead of attackers.
Navigating Regulatory & Compliance Complexity
With NIS2, DORA, SEC regulations, and other global mandates becoming more prescriptive, CISOs need to stay ahead of compliance changes—but these evolving policies also present an opportunity to strengthen security programs.
Sessions will focus on:
How regulatory frameworks are reshaping security practices across industries
Key compliance challenges for global organizations and strategies for staying ahead
The intersection of security, policy, and business risk—how to turn compliance into a competitive advantage
Sabeen Malik, Rapid7’s VP of Global Government Affairs & Public Policy, will help demystify cyber regulations, compliance challenges, and evolving data residency concerns in ‘From Chaos to Compliant: Demystifying Cyber Regulations’.
More to Come: A Full Day of Cybersecurity Insights
This is just a preview of the cutting-edge discussions, expert panels, and strategic deep-dives planned for Take Command 2025. Across the day, you’ll also hear from Rapid7’s own SOC experts, product leaders, and security researchers, who will provide real-world insights into:
What’s next for AI-driven security operations
How real-world attack simulations are changing security strategy
Inside the SOC: Expert stories from frontline threat hunters
Whether you’re a practitioner, security leader, or researcher, this event is designed to give you the insights and strategies needed to strengthen your security posture in 2025 and beyond.
Register Now to Take Command
Take Command 2025 is a free, global, virtual event happening on April 9. Don’t miss your chance to hear from security leaders and experts on the biggest challenges shaping the industry.
Swami Nathan has a track record of building new teams from scratch for global companies. Through his experiences, he’s identified what it takes to build not just any team – but a high performing team that drives innovation and growth for business while propelling career trajectories for those who take the ride. His experience in breaking down silos in tech, driving optimization, and increasing developer & business agility make him the perfect fit to lead the Rapid7 team in Pune, India.
“In today’s world, innovation in areas like Artificial Intelligence and Machine Learning are fundamentally changing the technology landscape at a rapid pace. We need to think about ways to become more nimble in our products, our engineering, and in our ability to listen to our customers so we can stay ahead of the curve. At Rapid7, we want to be on the forefront of this evolution, so we can continue to deliver value to our customers and build a more secure digital future.”
Building excellence through collaboration
Rapid7’s culture of collaboration, continuous improvement, and customer centricity provides the ideal environment for building exceptional teams. This environment creates unprecedented opportunities for those seeking to advance their careers and make meaningful contributions through their work.
“When you join a company, you are automatically part of a team. Becoming a high performing team requires a lot of work on the ground, and it’s a transformational journey every colleague must participate in. Along the way, there is a unique opportunity for every person to uplevel their skills and their profile. The experiences and unique challenges you are going to have, with a company that has the right culture and support systems in place, in an industry where there is an incredible amount of innovation, create an opportunity that not many people have access to, in their careers.”
Characteristics of high-performing teams
Swami shares a few key characteristics that stand out among high performing teams.
They challenge limitations
Some teams have an imaginary boundary when it comes to what they can or cannot do. On a high performing team, there is no boundary to what is possible. Instead, they will question limitations and ask, ‘why not?’
They demand excellence.
As the team begins to grow, they will not accept a B or C level player to join their team. Instead of wanting to be the smartest person in the room, high performing team members actively seek out colleagues they can learn from and who will contribute to the high level of performance.
“There are a few natural side effects when these things happen. First, you improve talent density across your entire company. Green employees are ramping quickly and learning from experts. Seasoned employees are simultaneously coaching those around them, while continuing to uplevel themselves. Second, you drive engagement and collaboration. High performing teams are inspired by the people they work with. They get up in the morning and are motivated for the day ahead because they genuinely look forward to coming to the office and collaborating in person.”
Essential qualities for success at Rapid7
As Rapid7 builds our team, there are key qualities they look for in candidates. For engineers and developers specifically, Swami shares the characteristics he looks for.
Product ownership
Building a product requires a variety of teams who are experts at different phases of the process. Instead of caring solely about their own domain, it’s important for engineers to have a sense of shared ownership over what they are delivering to customers. Great developers may not know everything about QA and testing, but they care enough about what they deliver to understand their role in building a quality product.
Do they have a growth mindset?
The ability to learn and take feedback is essential, especially for those who are early in their career and have not yet developed their technical skills. Being brave enough to ask questions and challenge the status quo will lay a foundation upon which they can build their technical skills.
Impact Through Influence and Action
Having the ability to influence is oftentimes associated with hierarchy or title. Swami challenges this belief and shares that if you have a point of view, are well researched, and can speak intelligently to your stakeholders, these are the factors that determine impact, regardless of your title. A bias for action means that you are looking to take the next step. You are proactive in moving things forward, breaking audacious goals into smaller milestones and action items. If someone can possess these two abilities, Swami knows they are someone who is capable of driving incredible impact in their team, and across the business.
What drew him to Rapid7
Swami joins as the first official full time employee of Rapid7 in India. So what was it that inspired him to take this new role? He credits the experience he has with company executives, and a shared system of beliefs and values with his decision to take the helm in Pune.
“As I was talking with the CEO, and our executive teams, the topics we spoke about did not feel like a traditional interview. Instead, we talked about who we each were as people, and what Rapid7 stands for as a company. As those conversations continued, I was pulled into the culture very naturally. Having a new office in India be strategically tied to the mission and purpose of the business, and how it will help drive such a positive impact for our customers was something that was really inspiring for me.”
Beyond the executive team, Swami shares a common thread that speaks to the company culture and values in action. “My experiences with the executive team and with other leaders across different business areas are all very consistent in terms of how they envision the future of our business. People willingly share information and historical context on their area of expertise, which gives me valuable insights into what we are working to achieve, and what we need as we build our team. It’s not easy to build this kind of consistency in a global organization, so that has continued to impress me throughout my journey here.”
Why join Rapid7 in India?
“What we are looking to do at Rapid7 India is impressive. We are planning for rapid growth this year (which by the way, is less than 10 months!). We don’t want to just build an office in Pune to grow our company headcount – we’re focused on growing high quality talent in a way that enables us to have a positive impact on customers, and deliver to critical business needs. This is a transformational journey that you won’t have anywhere else. We’re thrilled to offer the chance to be one of the first team members in India, contributing to a high performing team, experiencing tremendous personal growth, and delivering critical products and services to our customers.”
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.