Post Syndicated from Explosm.net original https://explosm.net/comics/pinocchio
New Cyanide and Happiness Comic
Post Syndicated from Explosm.net original https://explosm.net/comics/pinocchio
New Cyanide and Happiness Comic
Post Syndicated from xkcd.com original https://xkcd.com/3256/
Post Syndicated from Matt Granger original https://www.youtube.com/shorts/N-uT0flXb5U
Post Syndicated from Ryan Smith original https://www.servethehome.com/nxp-computex-keynote-2026-coverage/
The final keynote for Computex 2026 comes from NXP, where CEO Rafael Sotomayor is talking all about what it takes to deliver AI for edge devices and robotics in the real world, and how NXP is well-positioned to accomplish this
The post NXP Computex Keynote 2026 Coverage appeared first on ServeTheHome.
Post Syndicated from Explosm.net original https://explosm.net/comics/grateful
New Cyanide and Happiness Comic
Post Syndicated from Oglaf! -- Comics. Often dirty. original https://www.oglaf.com/lolth/

Post Syndicated from Cliff Robinson original https://www.servethehome.com/a-40-node-1u-cluster-gigabyte-r1c7-k0a-as1/
At Computex 2026, we found the Gigabyte R1C7-K0A-AS1 which can put 40 nodes with 320 cores, 40 iGPUs and 80 SSDs in just 1U
The post A 40-Node 1U Cluster Gigabyte R1C7-K0A-AS1 appeared first on ServeTheHome.
Post Syndicated from Боян Юруков original https://yurukov.net/blog/2026/ezok-gid/
Преди три години описах как може да се поръча през интернет европейска здравноосигурителна карта или ЕЗОК и да ви я доставят с куриер. Година по-рано такъв процес не съществуваше, но с упорство и няколко месеца разговори с НЗОК все пак изпълниха Закона за електронно управление и ми изкараха карта поръчана през Системата за сигурно електронно връчване.
В края на 2024-та въведоха по-лесен начин за поръчване – с формуляр, който събира сам нужната информация и изпраща съобщение на районната каса. Описах процеса, обнових първата ми статия и доста хора се възползваха. Все пак, към средата на миналата година под 6% от всички извадили такава карта използваха електронния формуляр. Повечето все още предпочитат да чакат на опашка в банка по два пъти за това нещо. Тогава описах данните за изваждането на картите, защо един единствен кандидат от БСП все печели обществената поръчка за милиони и защо НЗОК са решили, че трябва да я обновяваме всяка година.
Една от причините хората да ходят на място, която беше коментирана под предишните ми статии, е грешките във формуляра. За съжаление, има още много какво да се желае от работата на Информационно обслужване по тези точки. Затова описвам тук подробно със снимки какво трябва да се направи и как да преодолеете основния проблем, за който им писах.
Първо, трябва да имате предвид тези неща:
Повече за тези и други условия може да прочетете на страницата на НЗОК. Повече за самата електронна услуга ще намерите тук.
След като отворите формуляра ще иска да влезете в портала на egov. Най-удобно е това да стане с ПИН на НАП, но може и с някой от електронните подписи. За съжаление, електронната идентичност все още не е осъществена на държавно ниво, най-вече заради блокиране от страна на МВР и лобизъм. Ако за пръв път влизате, може да ви иска да си направите профил, но няма нужда да въвеждате нищо освен навярно мейл адрес.
След това минавате през тези екрани. Сменяйте снимките им със стрелката надясно в галерията.
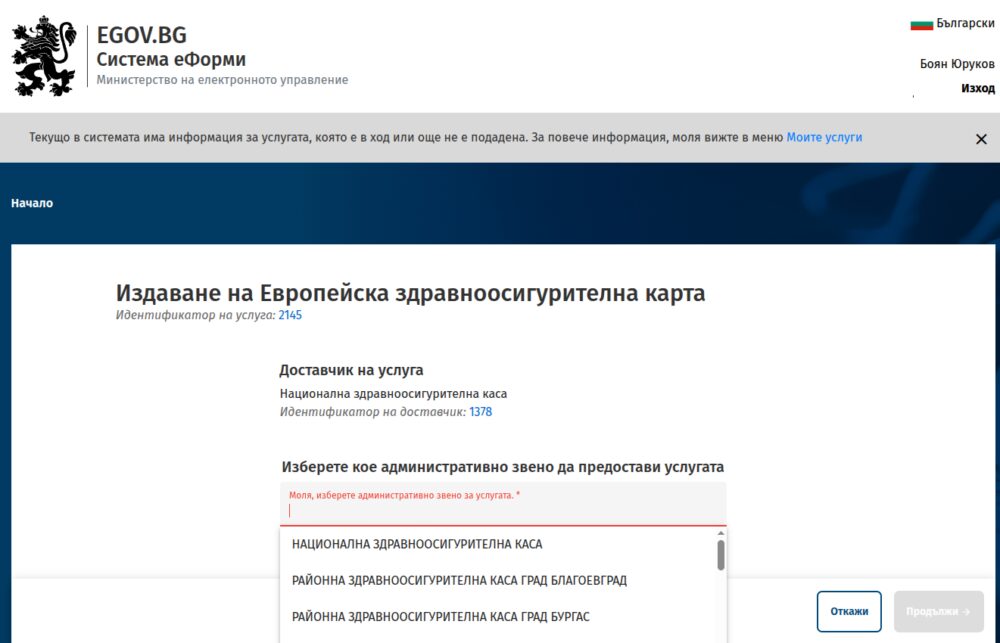
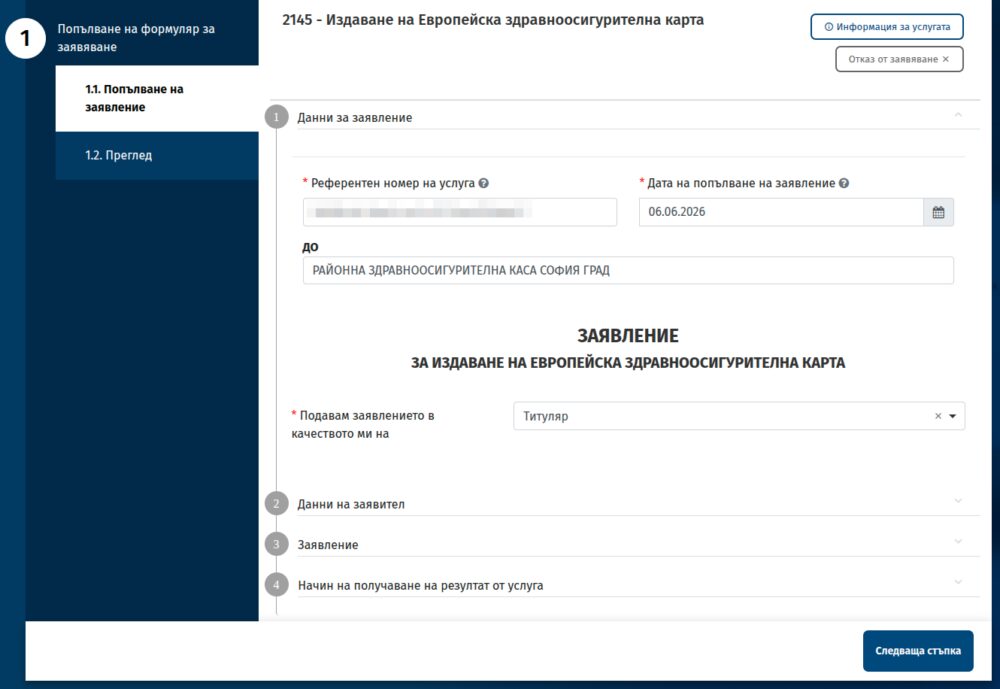
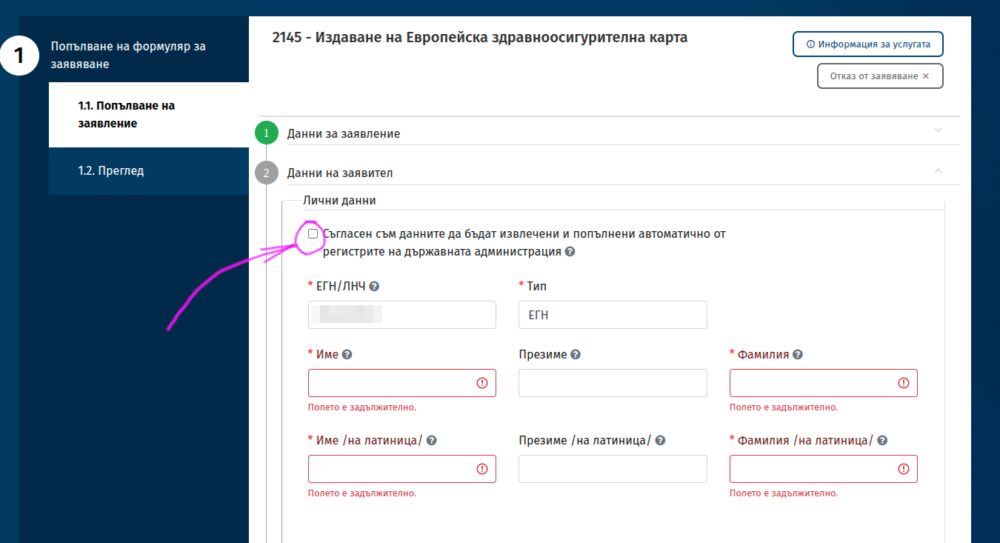
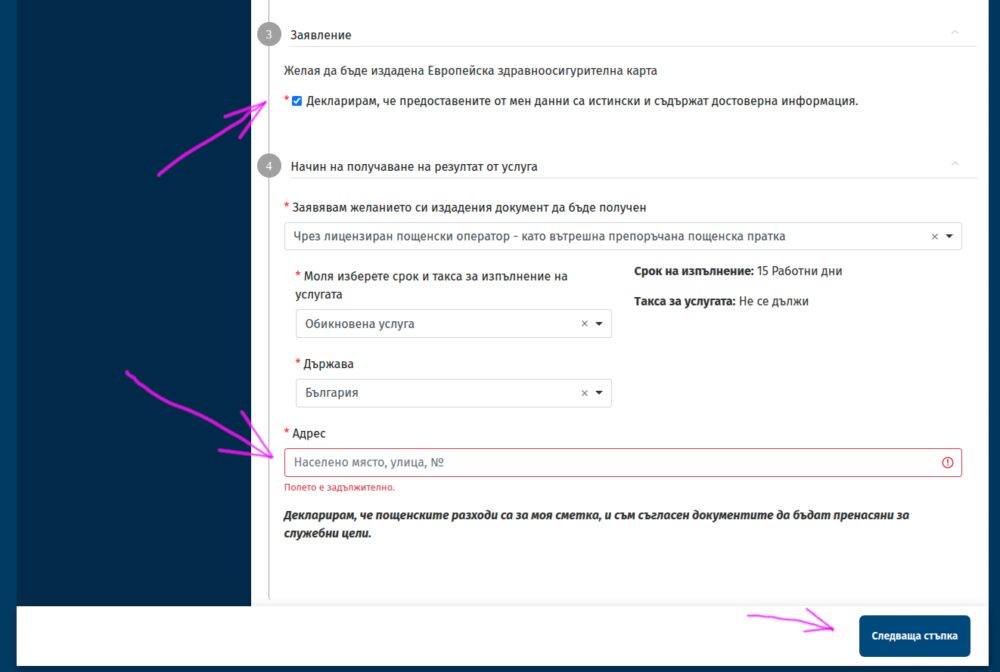
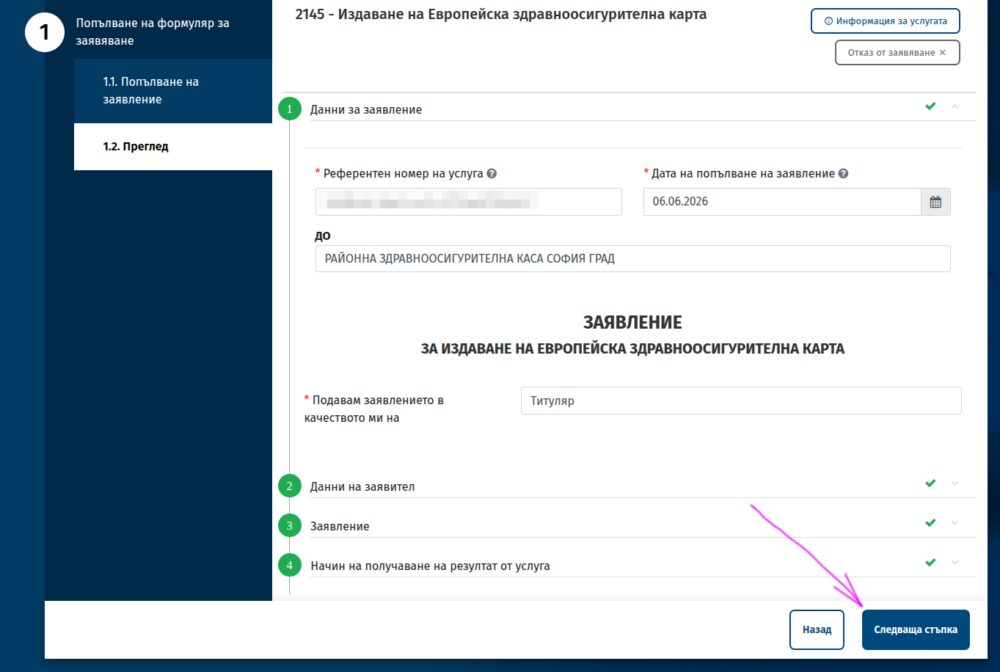
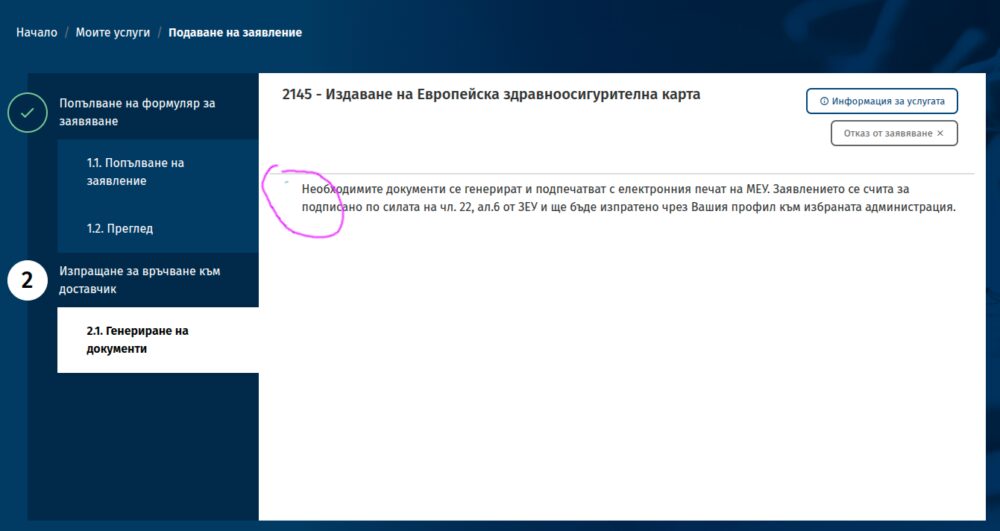
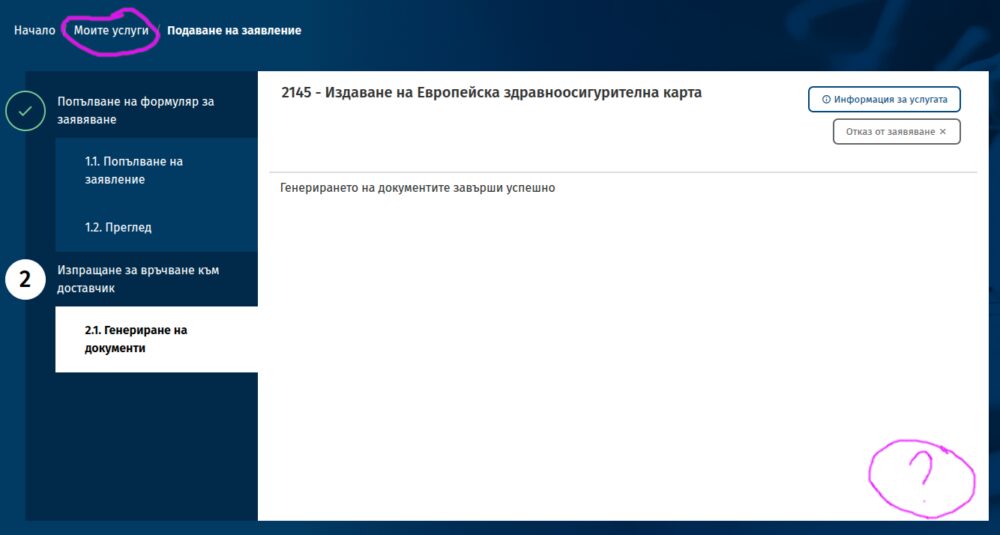
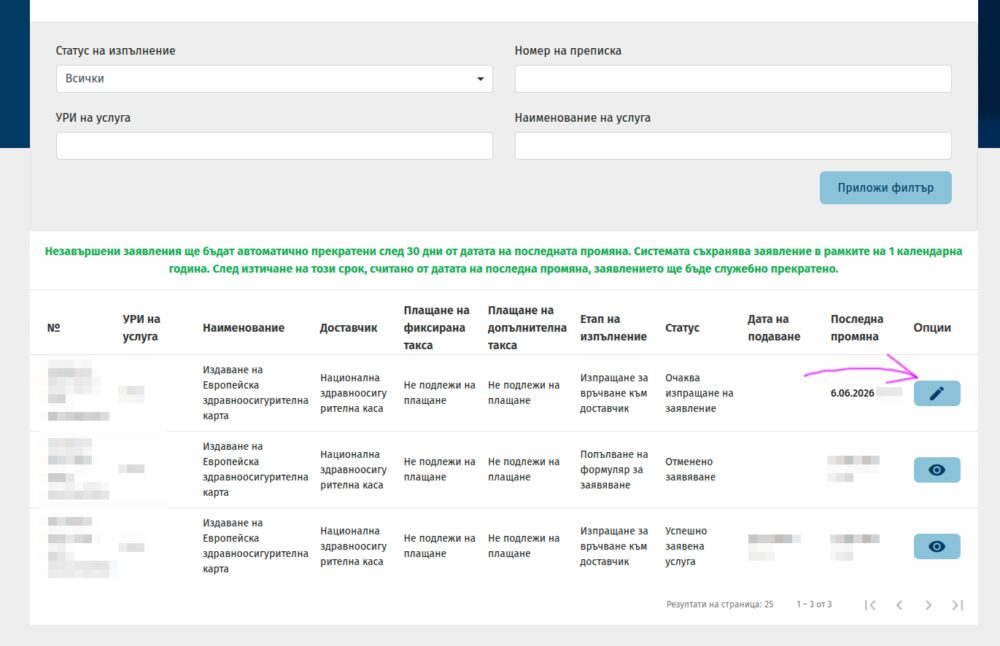
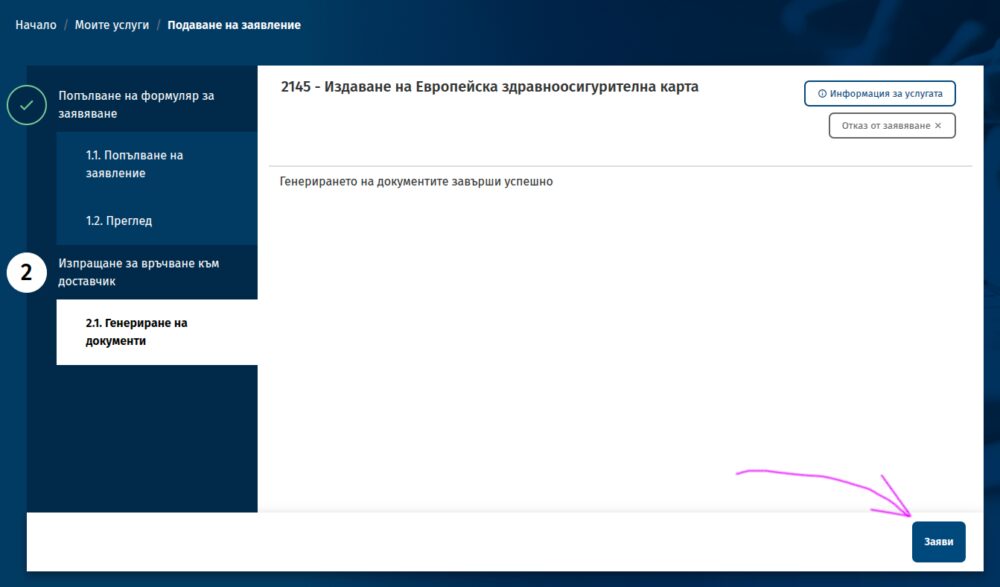
Най-честата грешка в работата на формуляра е, че не се появява бутонът за изпращане на генерирания документ. Тогава трябва да натиснете „Моите услуги“ както показвам горе, за да отворите списъка с вашите формуляри. Ще ви пита дали сте сигурни, защото сте щели да загубите въведеното – не е вярно, не се губи. Като натиснете бутона с молива на последния формуляр ще се отвори същата страница, но вече с бутон за изпращане. Натискате го.
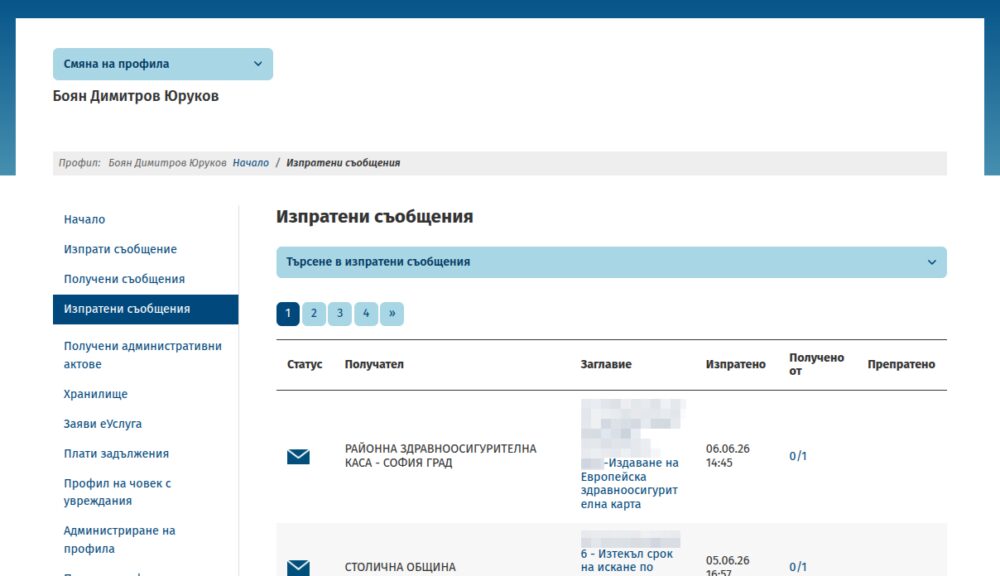
Може да потвърдите, че формулярът е изпратен като отворите ССЕВ и намерите в изходящи попълнен документ към районната здравна каса.
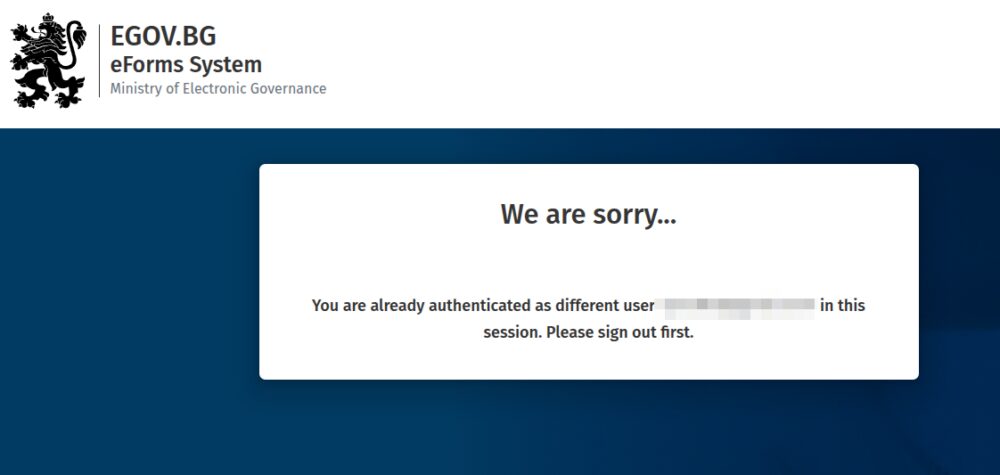
Друга честа грешка е, ако се опитате през няколко различни профила един след друг да подадете заявления. Няма значение дали сте излезли от стария профил, системата на EGov конкретно за формулярите може да ви покаже нещо като това олу. Оправя се като отворите формуляра в инкогнито прозорец. Ако се разровите в адресите в опит да се разлогнете отново, най-много да откриете, че Информационно обслужване си е забравило куп начални страници по подразбиране и линкове към админ панели, което никога не е добра идея.
Когато отворите формуляра, е възможно да видите съобщение в червено, че има проблем със ССЕВ. Вчера това се беше случило, независимо, че цял ден изпращах съобщения през същата система и нямаше проблем. Ако използвате ПИК на НАП и тази връзка пада понякога. Случва се и да не приема в някои дни електронни подписи.
Вероятността да хванете такива проблеми е малка, но не вдъхва особено доверие в усилията за дигитализация на държавата и работата на ИО в сегашния си формат (и ръководство), когато се случи точно на вас. Когато използвате почти всеки ден тези портали се сблъсквате с това поне веднъж седмично. Замислете се как нещата може да се случват по-добре и опитайте по-късно.
През октомври ще искам пак данните на извадилите ЕЗОК през годината и начина на подаване на заявлението. Ще е интересно дали и тази година ще видим увеличение, както миналата.
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/HPlAPDHXI4g
Post Syndicated from Боян Юруков original https://yurukov.net/blog/2026/greece-toll-2/
Доста хора отбелязаха в последните седмици, че са срещнали трудност при поръчването на транспондери за бързо минаване на тол станциите в Гърция. Миналия януари описах колко е лесно да се поръча такъв RFID чип, да се захрани с пари и да се избягват опашките.
В последните седмици след промени в структурата, конкретно EgnatiaPass вече не може да се доставя извън Гърция. Потвърдих това с тях. Не планират в близко бъдеще да възстановят доставките. Не ми е известно и някой от другите доставчици да позволяват такава опция. Ако имате вече такъв чип, то той ще работи. Акаунта и сумите, които сте заредили, се пазят и нищо не се променя. Просто за нови клиенти са спрели възможността да получат чипа в чужбина.
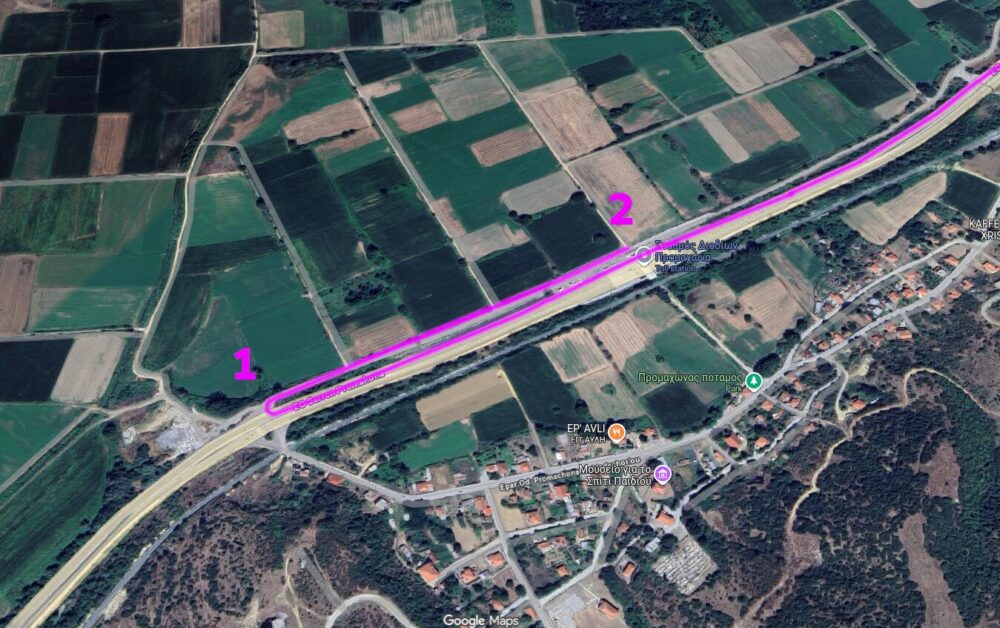
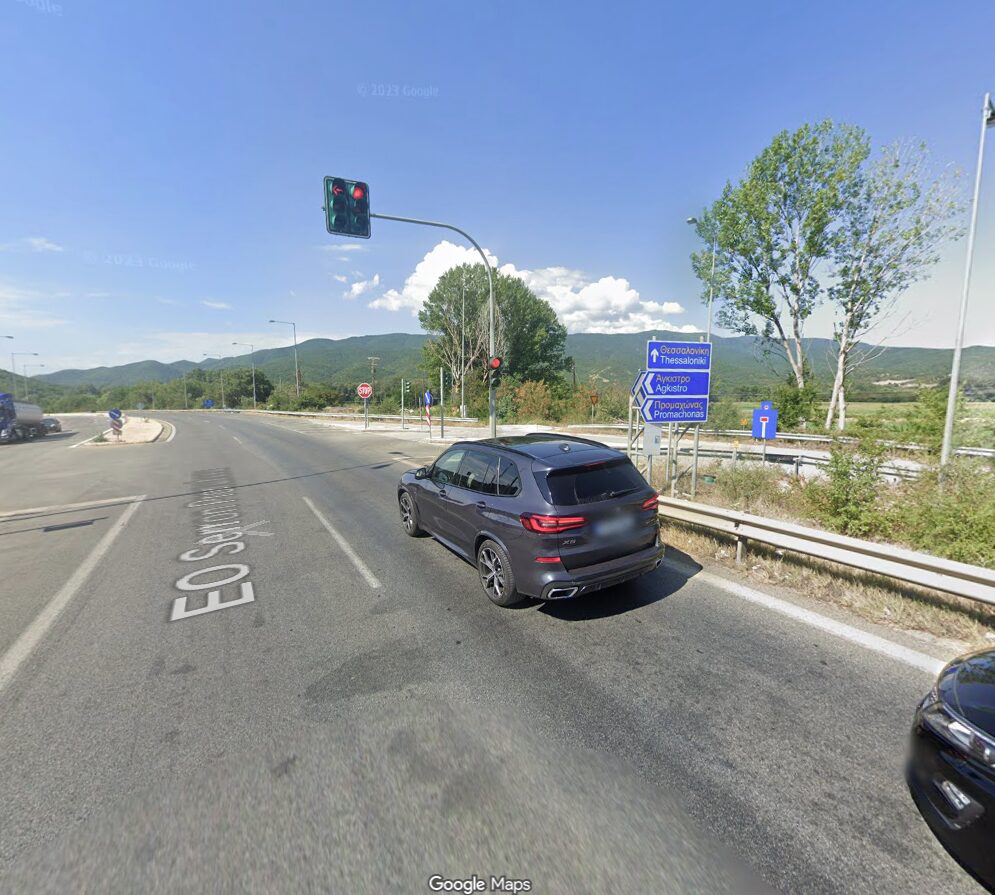
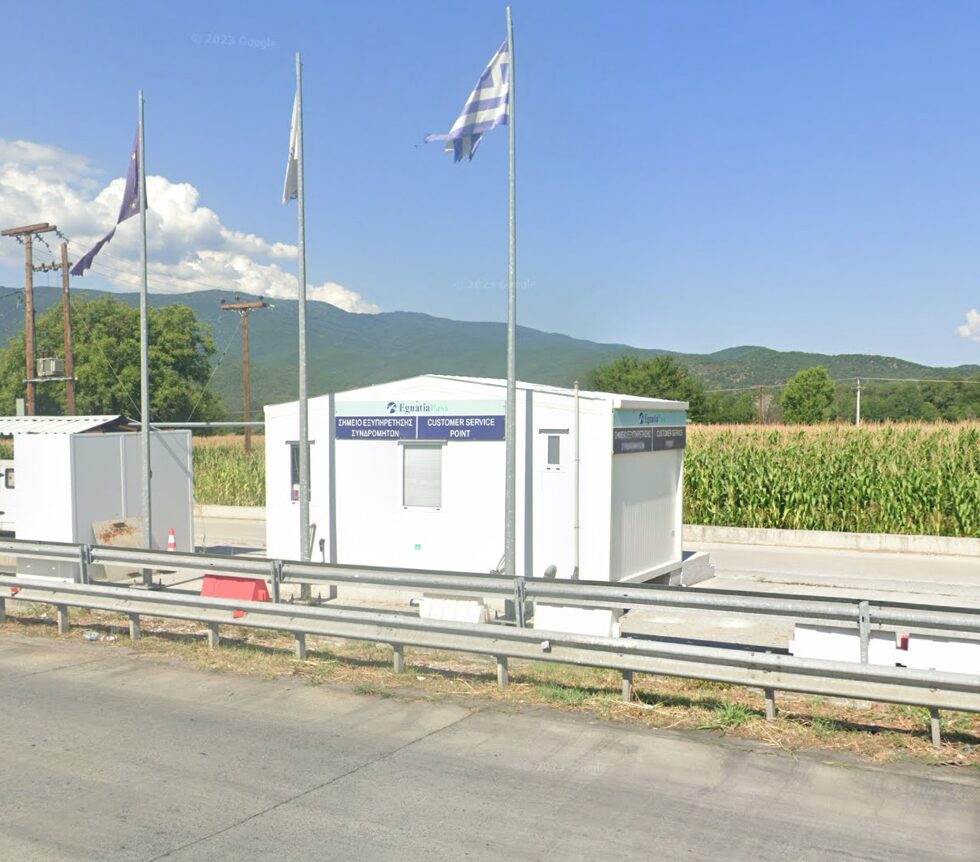
Затова единственият вариант остава да го вземете на място. Най-удобно за целта специално за EgnatiaPass е да го вземете още на първата тол станция след кулата. По техните инструкции като минете тол станцията Promachonas след Кулата, на първият светофар няколко стотин метра по-нататък завивате надясно се връщате по локалния път и ще намерите паркинг и будка на Egnatia точно до тол станцията. Там може да попълните документите и да получите чип. Според центъра за клиенти нямало нужда да се попълва нищо предварително през online формуляра – всичко се прави на място. На снимките долу се вижда какъв е пътя и как изглежда мястото.
Не намерих такъв център за клиенти при Маказа. Ако знаете други доставчици на такива танспондери с други удобни места за взимане или дори някои, които доставят в България – споделете.
Припомням също, че е много добра идея да си извадите или ако имате – да си обновите европейската здравна карта. Тя може да се поръча изцяло online и достави с куриер, макар и да трябва да я обновяваме всяка година за възрастни.
Post Syndicated from Боряна Телбис original https://www.toest.bg/sedmitsata-1-6-yuni/
„Това дете няма много добър цвят, трябва да отидете веднага до болницата и да му изследвате билирубина“, ми каза Ася Демирева (която Ина Иванова ви представя в „Тези хора“), когато я бях повикала на консултация за втория ми син.
Детето беше с цвят „Тръмп“, да се разбира – жизнерадостно оранжево, с което и се изчерпваше цялата жизнерадост на ситуацията. Защото после се оказа, че лекарите имат съмнения за чернодробна недостатъчност, и бебето беше хоспитализирано в неонатологията само две седмици след раждането. Беше особен момент: занесох до входа на отделението дете, отвориха вратата, взеха ми го, затвориха вратата, после пак я отвориха, за да ми пуснат в шепите миниатюрните му дрешки и да ми кажат, че свиждането е всеки ден от 16:00 до 16:30.
Всичко ти се сгромолясва за секунди и после спешно намираш сили да го изградиш отново, защото имаш още едно дете за гледане и работа за вършене. Човек малко оглупява в такива ситуации и е добре, че разполагаме с хора като Ася, които успяват да ни фиксират тук и сега.
 Ина Иванова
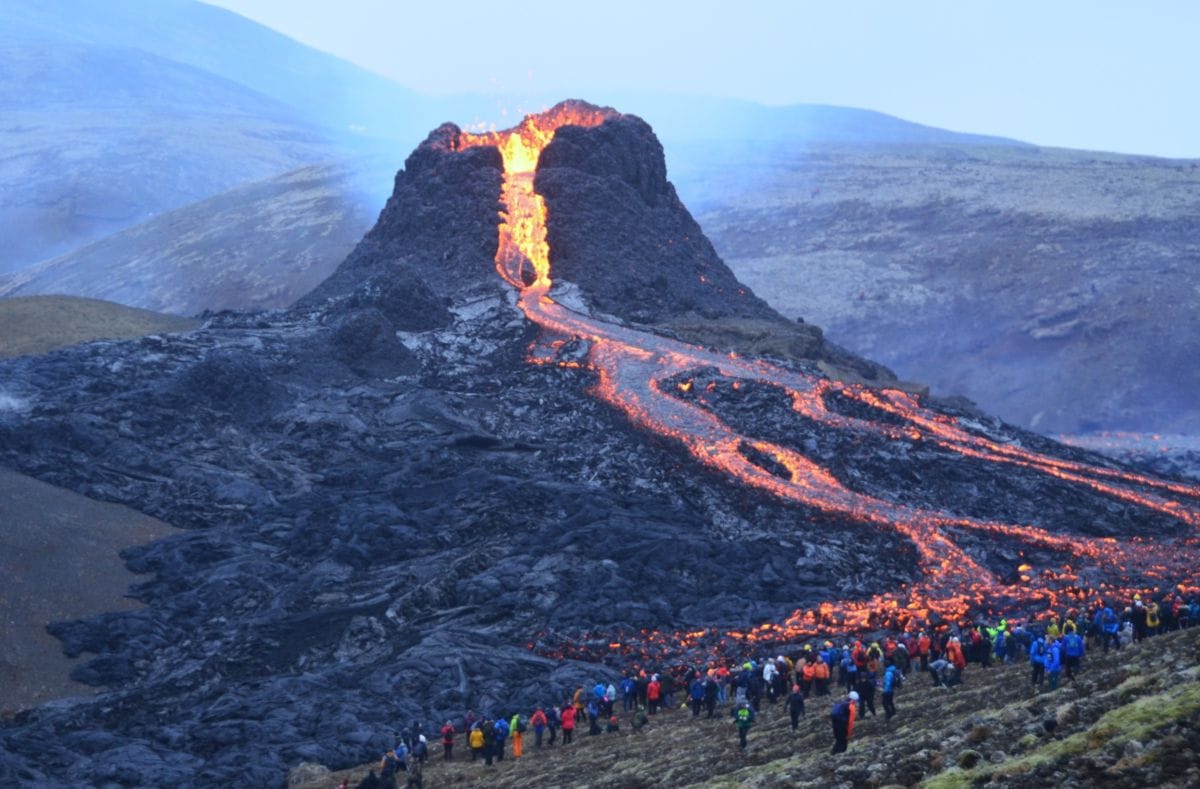
След личното лирическо отклонение, което не беше съвсем неоснователно, защото в крайна сметка успях да въведа в играта първия текст от тазседмичния брой на „Тоест“, тръгвам рязко на север. Оттам идва материалът на Светла Стоянова, който също е свързан със спасяването на човеци от човеци. Става дума за оказването на първа помощ на бедстващи хора в Исландия. От известно време Светла работи като хижарка в страната и ни разказва какво представлява тамошната спасителна служба.
От текста става ясно, че на всеки 100 исландци се пада по един доброволец от Исландската спасителна служба. Едва ли ще ви изненадам, но в България нещата не стоят точно така. Освен да си внесем исландци…
 Светла Стоянова
Исландци не сме си внесли, но копираме смело и сръчно американския опит по овладяване на медии през политики и регулации. Или може би те копират нашия? При всички положения има някакъв международен обмен (да живей, да живей!).
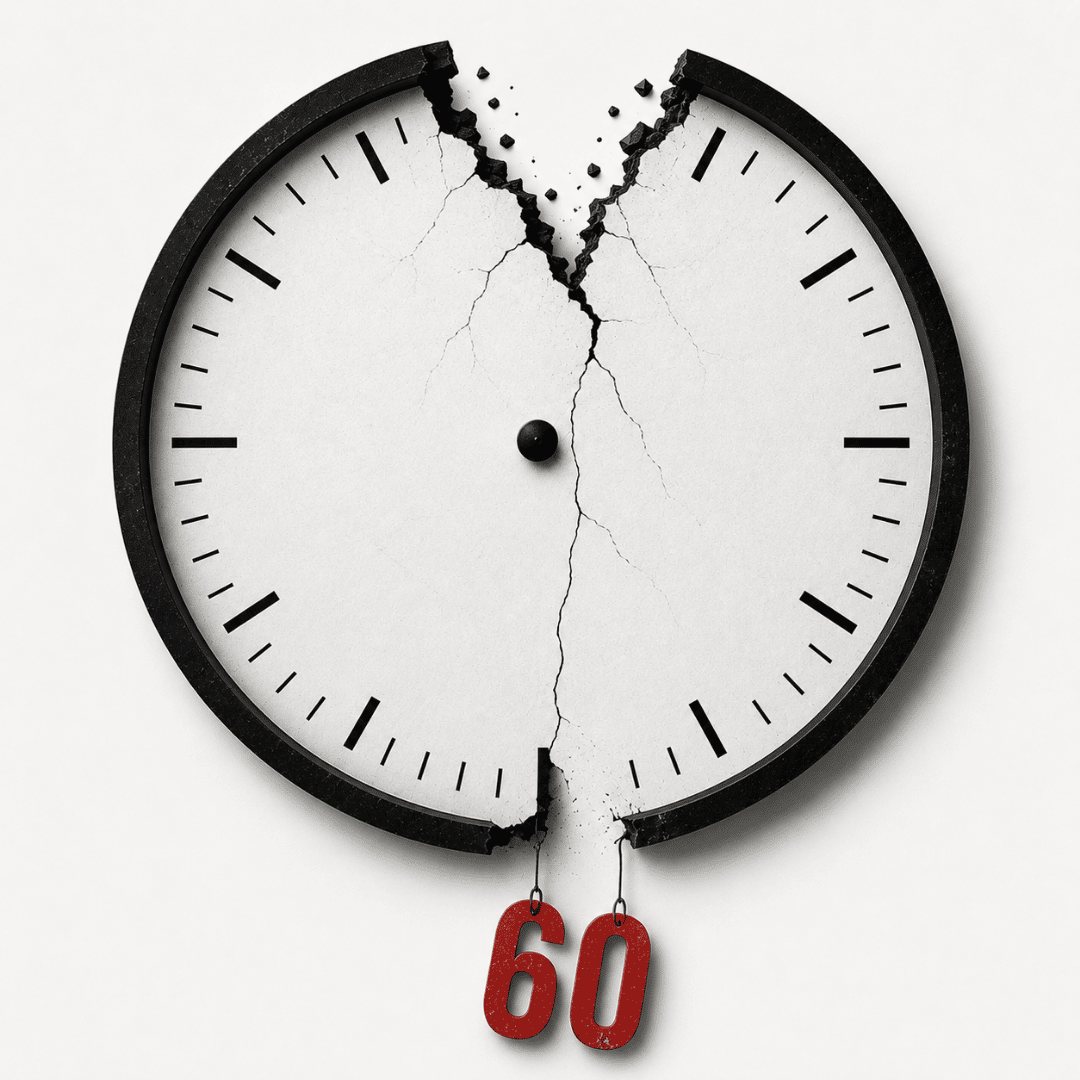
Тази седмица в текста си Good night, and good luck, motherf*ckers Дарина Сарелска ни разказва за обезкървяването на легендарното американско предаване „60 минути“, кулминирало с дисциплинарното уволнение на водещия Скот Пели. „Айде няма нужда да го жалим Пели“, би казал някой – и с право. Не жалим него, а по-скоро си даваме малко по-ясна сметка (заради мащаба) какво се случва с нашите медии. Ето малка част от текста на Дарина:
Ефирът става фасада, а журналистиката – разменна монета в една много по-голяма игра. Място, на което се изграждат отношения, печели се достъп и се договарят решения, струващи много повече от рекламното време между две новинарски емисии. Този завой в бизнес модела е далеч по-видим на малки пазари като нашия, където парите просто свършват по-бързо.
Големите търговски оператори у нас, като част от мултинационални компании с разнородни бизнес интереси, отдавна практикуват този модел. В него телевизията е само рекламна витрина, през която се отварят (или затварят) врати към далеч по-доходоносни сделки и индустрии.
 Дарина Сарелска
„Жива мизерия“, както каза във включване в сутрешния блок една от жителките на село Тича, чиято къща е пълна с кални наноси заради бедствието от нощта на 4 срещу 5 юни. „Жива мизерия“ потвърждавам и аз.
И като казах „бедствие“, веднага се сещам, че бюджетът на страната е в бедствено положение и Гълъб Донев ще трябва много добре да си подреди перата, за да вържем – не, но поне да приближим двата края. И това надали ще стане без надзора на Европейската комисия. За всичко това разказва Емилия Милчева в материала „Прогресът на Радев тръгва с остеритет“.
 Емилия Милчева
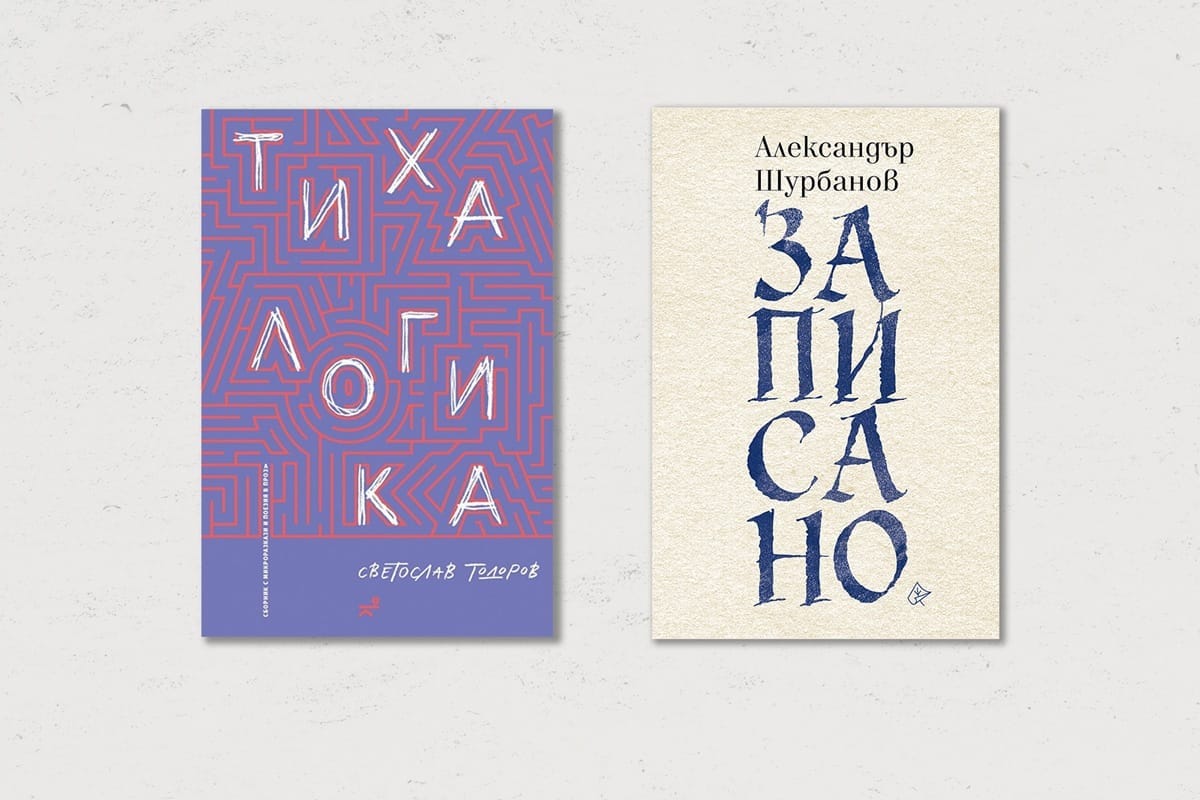
От бюджета минавам към буквите, по които и тази седмица се движи Зорница Христова в опит да си отговори на въпроси като: общуват ли помежду си литературните поколения; четат ли се едни други в книгите си; познават ли се изобщо? Книгите, за които ни разказва този път, са „Записано“ от Александър Шурбанов и „Тиха логика“ от Светослав Тодоров.
 Зорница Христова
Изисква се специален талант да разказваш интересно книги. Още по-специален е талантът да разказваш за книги, без да ги разказваш. Зорница Христова е майсторка в този занаят. Наскоро тя гостува на Владислав Севов в десети епизод на „Тоест разговаряме“. Ако по това време сте били заети, сега е моментът да се върнете към този наистина вдъхновяващ 24-майски разговор, който засега е последен в поредицата.
 Владислав Севов
Междувременно светът продължава да се държи така, сякаш няма намерение да забавя темпото. Климатът се променя, войните не свършват, алгоритмите стават все по-уверени в себе си, а хората все по-рядко четат нещо по-дълго от описание под рийл. Което е чудесен повод да направите точно обратното. В „Тоест“ се грижим за това.
Завършвам с текста на Теодора Станимирова, в който се разглежда въпросът защо Gen Z и Gen Alpha са все по-тревожни по отношение на климатичните промени и неизбежно някак стават по-ангажирани с климатичните политики. (То е ясно защо – за тях е въпрос на бъдеще, а за чичовците със златните рамки на очилата, дето притежават тецове и мини, е въпрос на все тая.) Чудесен материал на Теодора, в който се обяснява и защо природни бедствия като в Сливенско от тази седмица или в Габровско от миналата ще ни струват все по-скъпо – не само финансово.
 Теодора Станимирова
В петък сутринта гледах по телевизията как една репортерка нахлува от къща в къща в същото това село Тича – без да пита може ли, само с „На живо сме“, – за да ни покаже как всичко е потънало в тиня и как хората се опитват да си изгребат живота от подовете на къщите си, макар да не е много ясно как точно ще им се помогне, като ги показваме, но нейсе… В един момент пред нея се изправи някакъв слабичък човечец, когото тя застреля с „Как ще се справите?“, все едно очакваше ей сега да ѝ излезе с презентация или даже с TED Talk как точно ще се справят.
Той обаче ѝ каза само:
Бог ще помисли за всичко.
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/qr9SBzwXmrA
Post Syndicated from Channy Yun (윤석찬) original https://aws.amazon.com/blogs/aws/try-the-new-console-experience-in-amazon-bedrock-optimized-for-anthropic-and-openai-compatible-apis/
Today, we’re announcing a new console experience in Amazon Bedrock for you to experiment, iterate, and scale with the latest AI models on Amazon Bedrock’s next-generation inference engine built for high performance, reliability, and security. This console has a refreshed workflow optimized for bedrock-mantle endpoint, which supports the latest GPT, Claude, and open-weight models with the OpenAI Responses API, OpenAI Chat Completions API, and the Anthropic Messages API.
The new console experience makes it simple to find the right model and move quickly from evaluation to production.
How to get started
You can try a new experience by choosing Try the Bedrock Mantle Console from within the Amazon Bedrock console, or by using the new console link directly.
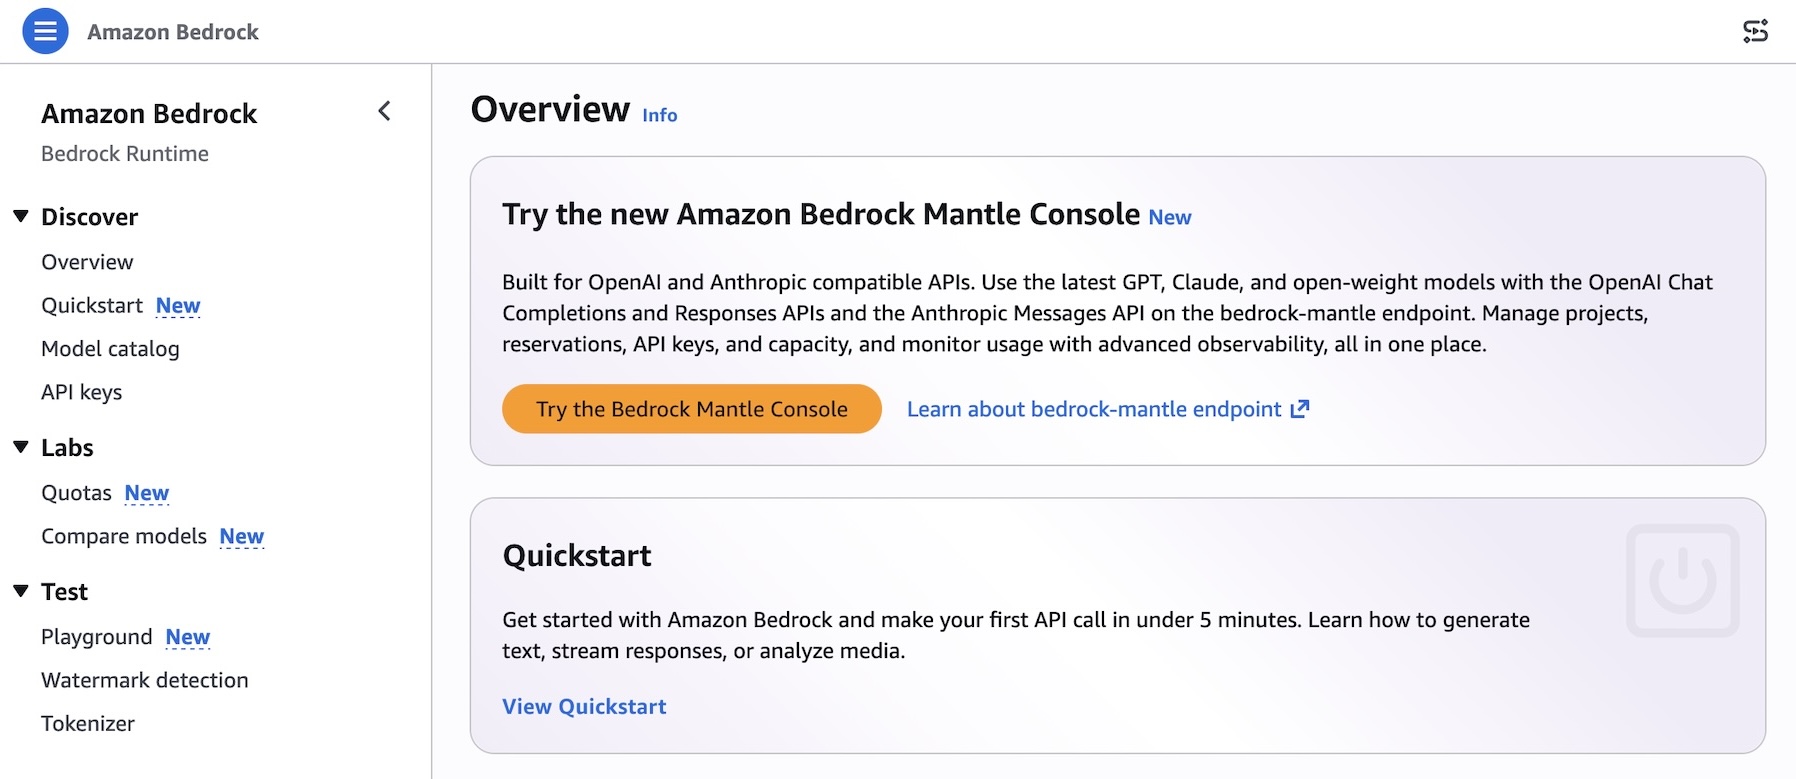
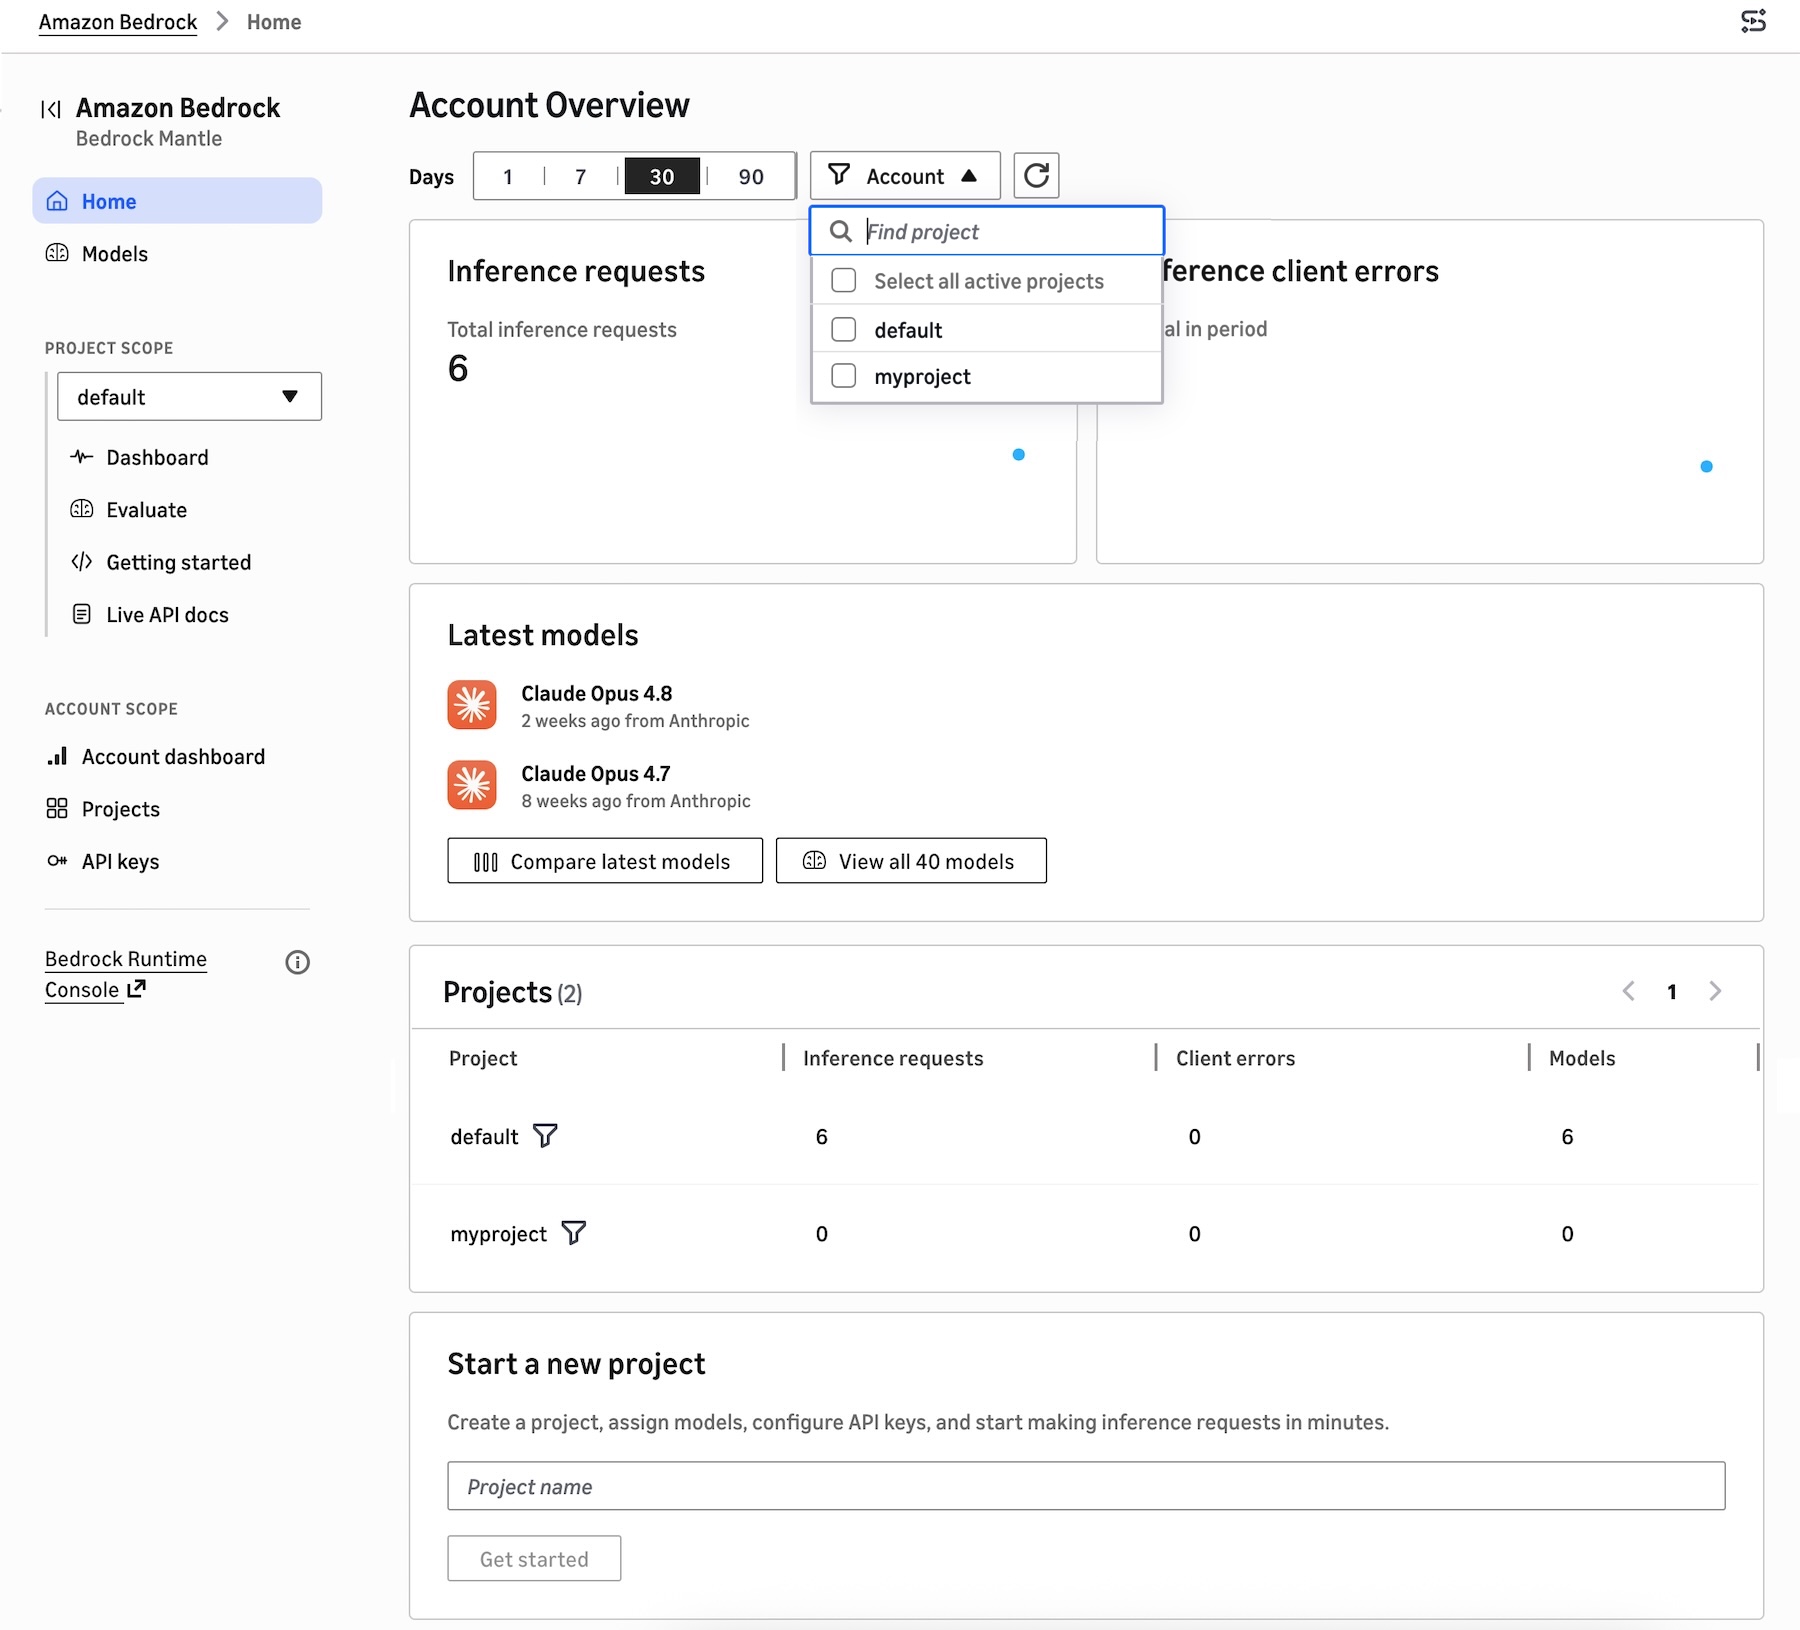
You can find a project-based dashboard to show inference requests and error by range of recent dates, recently used models, and the project list. You can create a project, assign models, configure API keys, and start making inference requests in minutes.
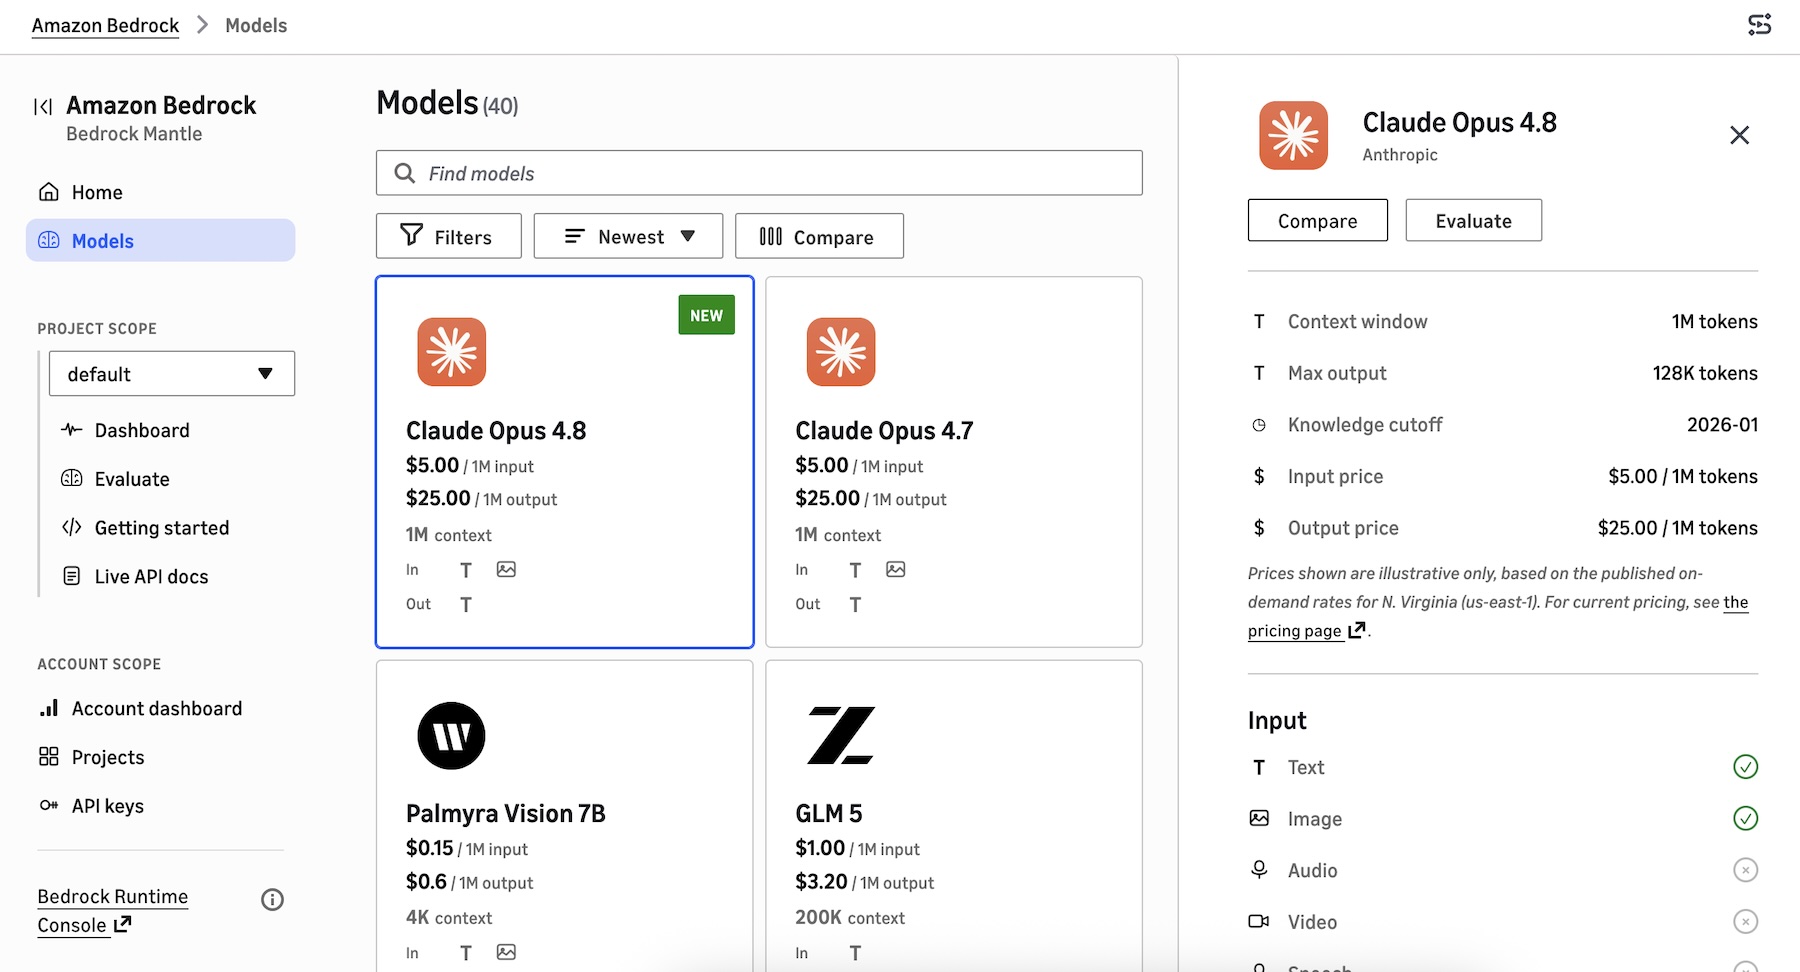
A new model catalog shows the latest GPT, Claude, and open-weight models that are supported on the bedrock-mantle engine. You can see the details of features, tokens, pricing, input/output, pricing information, and Regional availability. You can also compare up to 3 models in a single view.
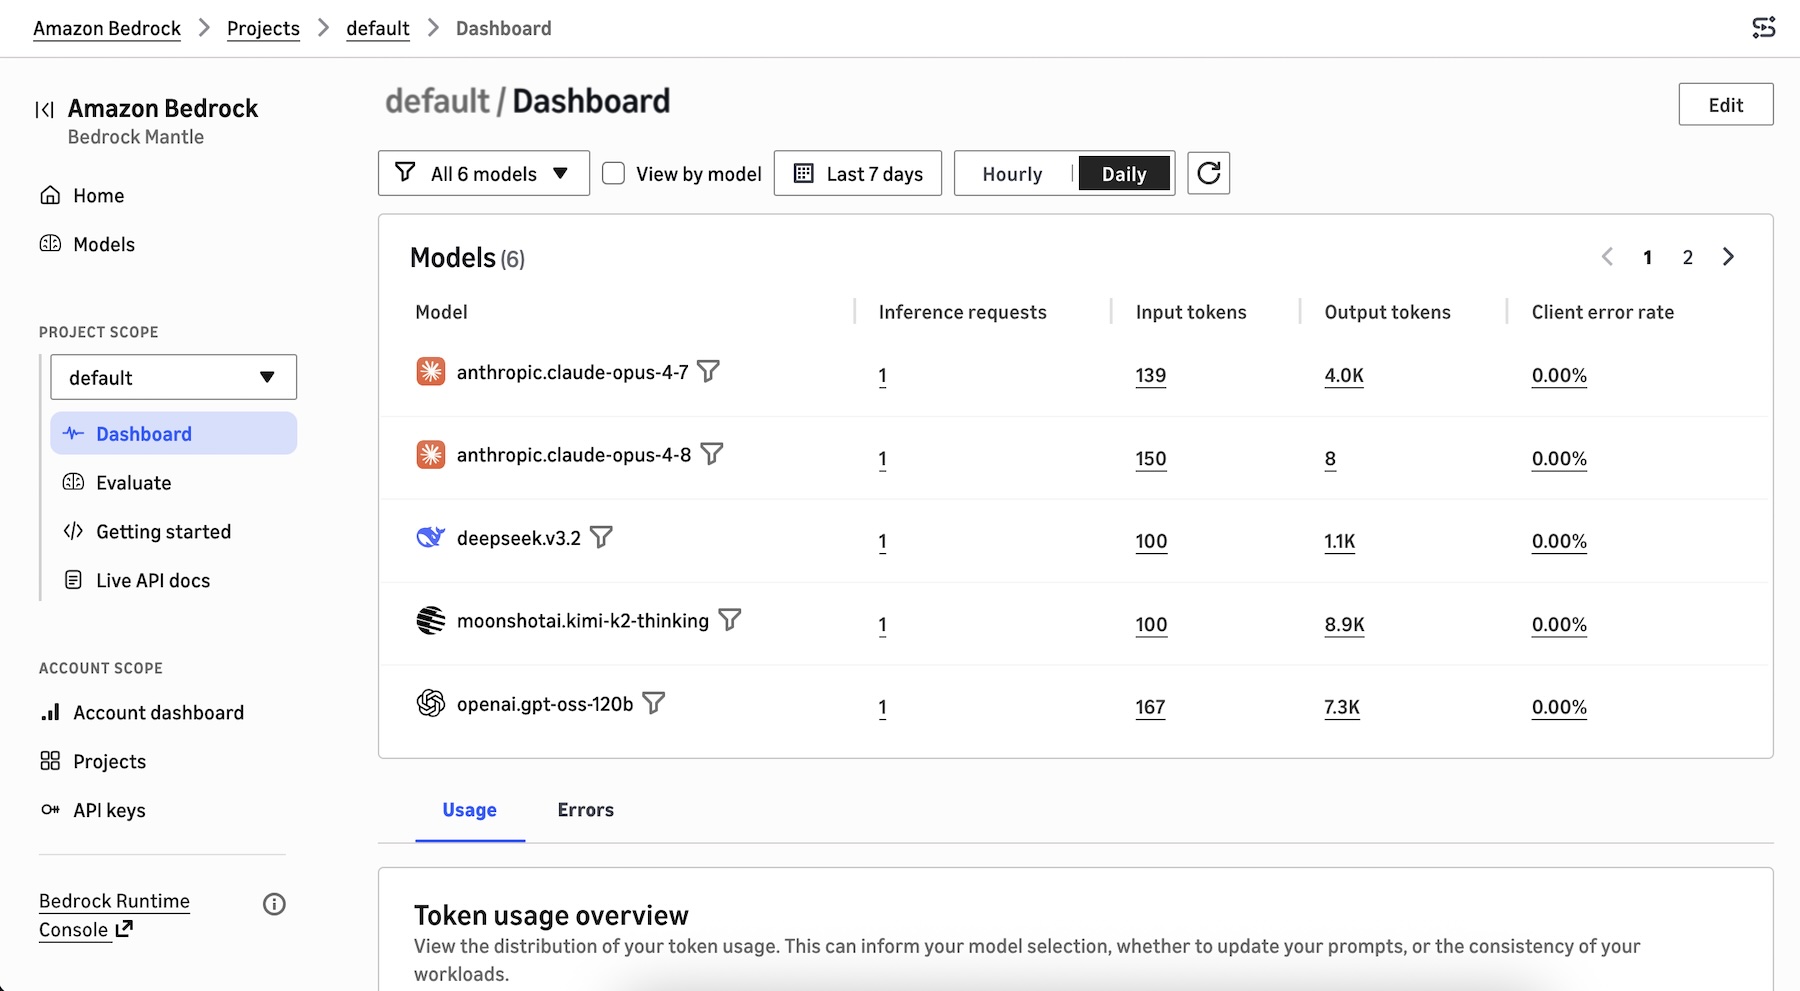
When you choose the project dashboard, you can see the models used in the project, the distribution of your token usage such as total token usage, token usage per minute, inference requests per minute, and tokens per inference request. This can inform your model selection, prompt optimization, and workload consistency decisions.
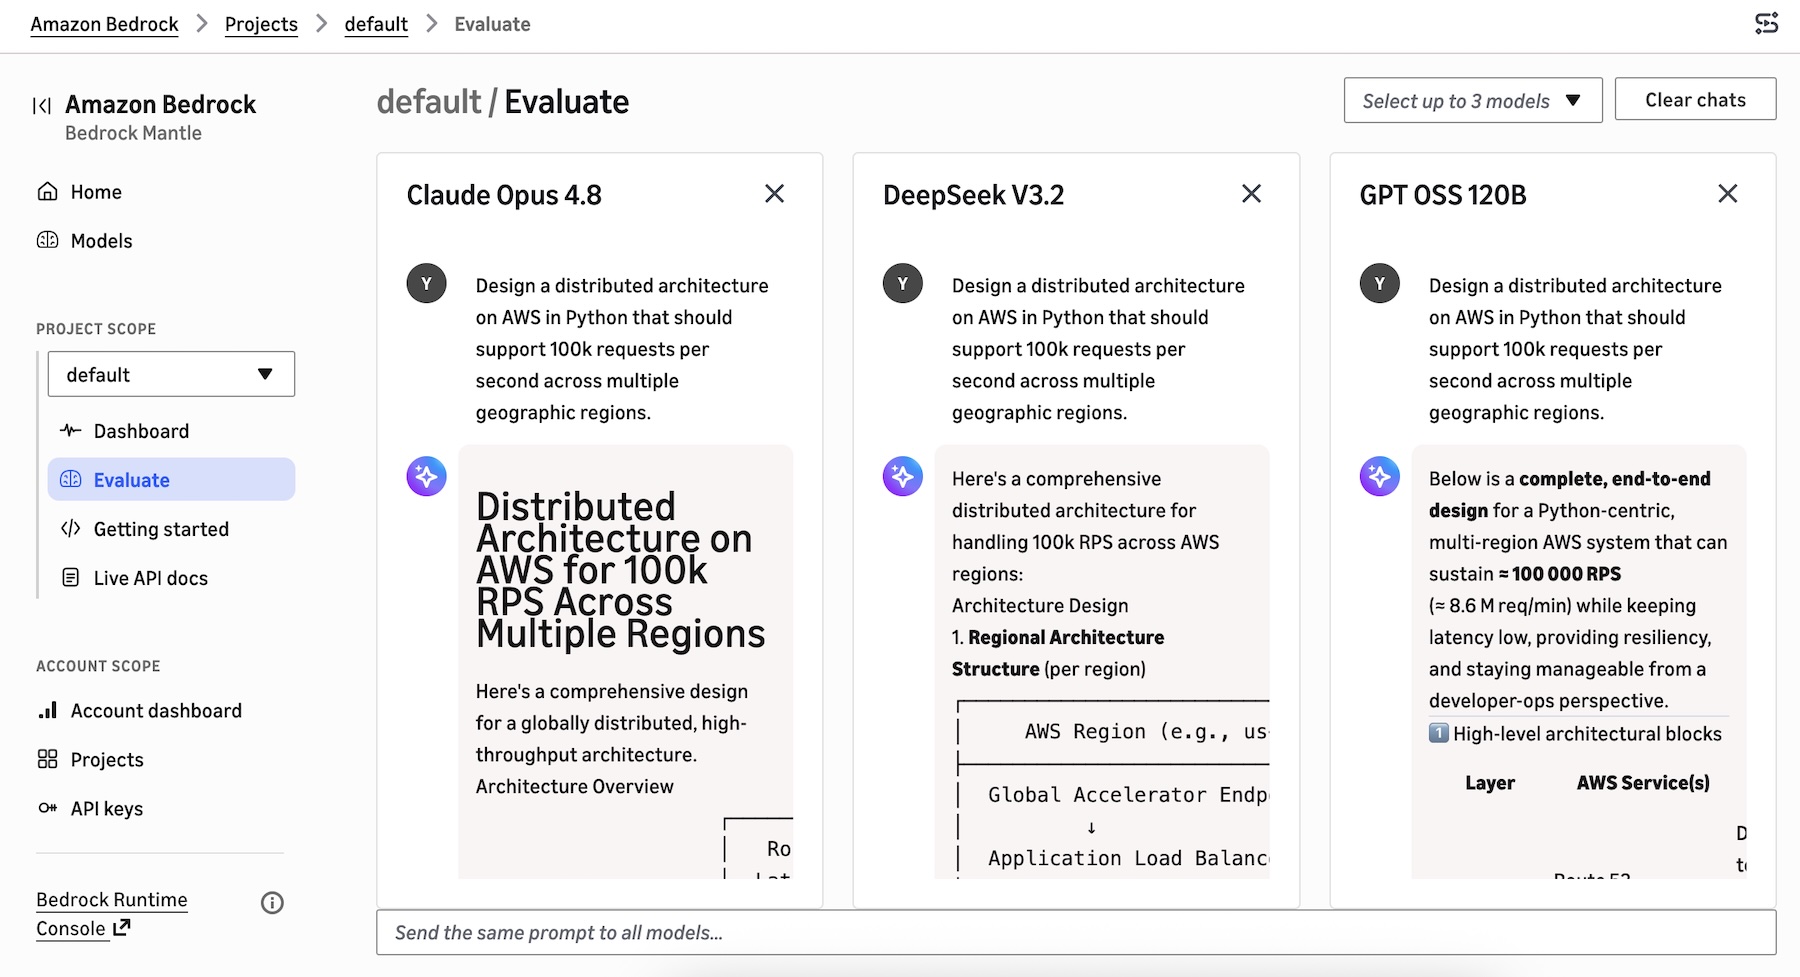
You can select up to 3 models to start evaluating to compare responses side by side with the same prompt.
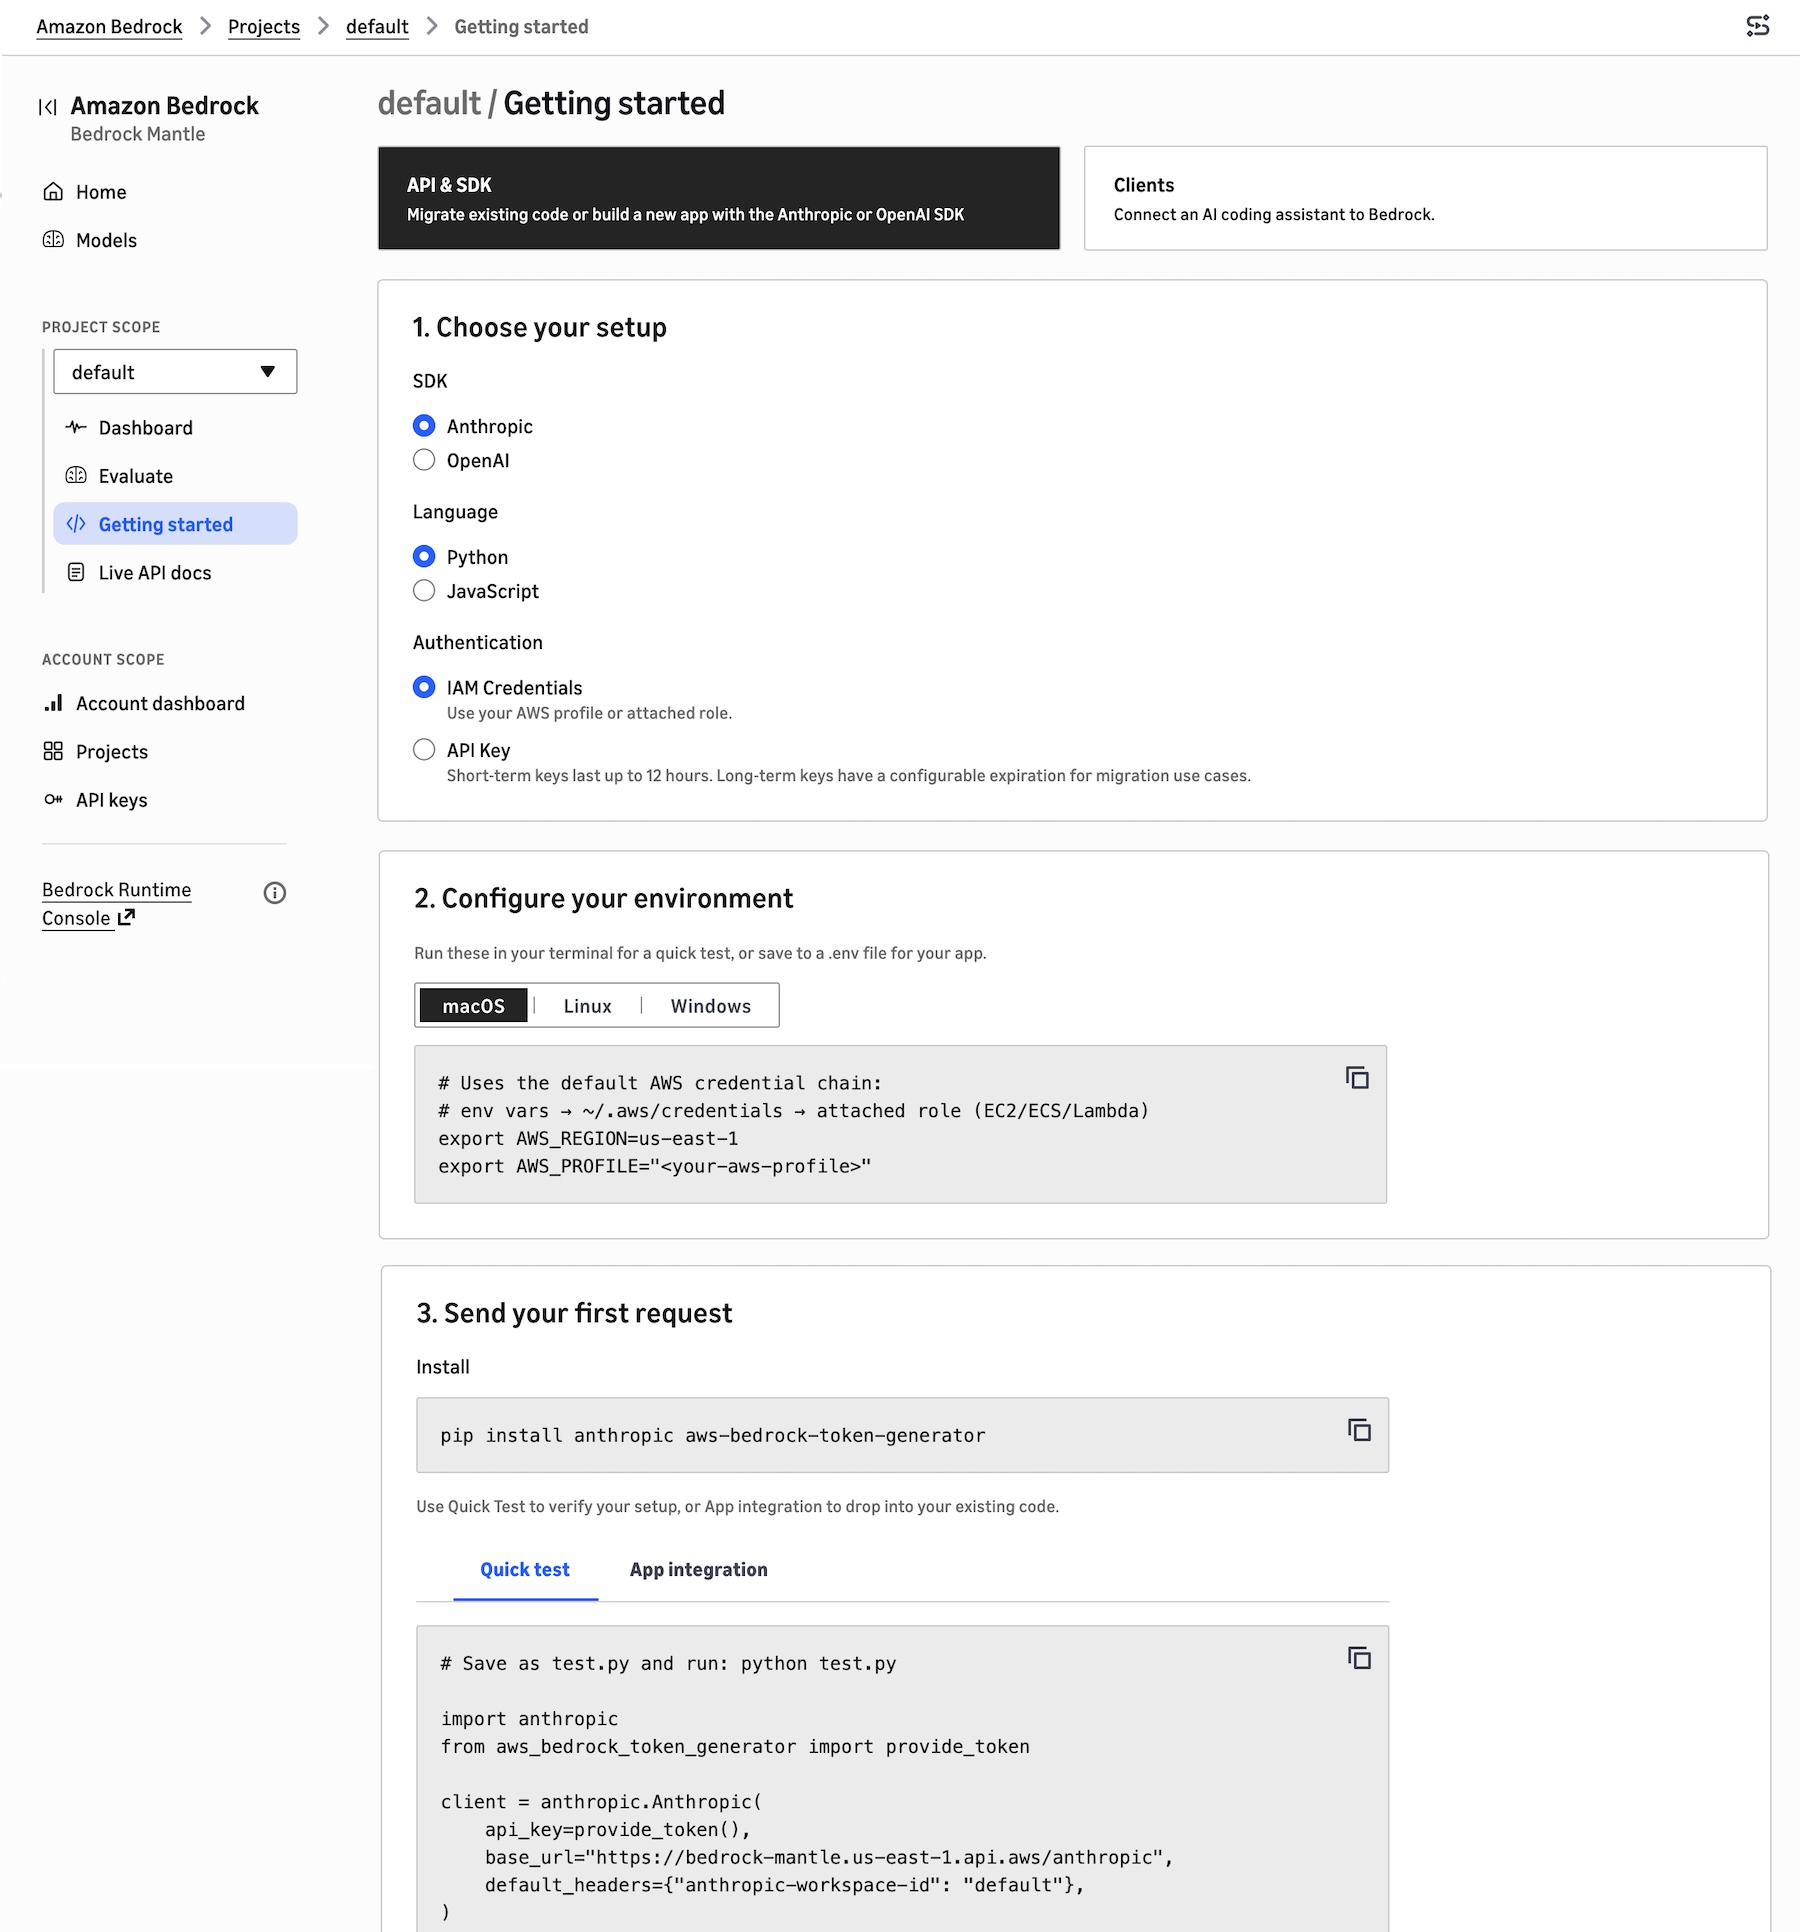
To build your application in the project, choose Getting started. You can migrate existing code, build a new app with the Anthropic or OpenAI SDK, or connect an AI coding assistant to Bedrock.
Choose the API & SDK, your SDK (either Anthropic or OpenAI), your preferred programming language, and your authentication method. It shows your environment code to run these in your terminal for a quick test, or save to a .env file for your application. You can also send your first request with sample code snippets to verify your setup.
When you choose Clients, you can select the AI coding agent source such as Claude Code, Cline, Codex, Cursor, or OpenCode that you want to connect to the bedrock-mantle engine. It provides instructions on how to install the AI agent, use your AWS IAM credentials or use a Bedrock API key, set environment variables, and route requests from each AI agent through Bedrock.
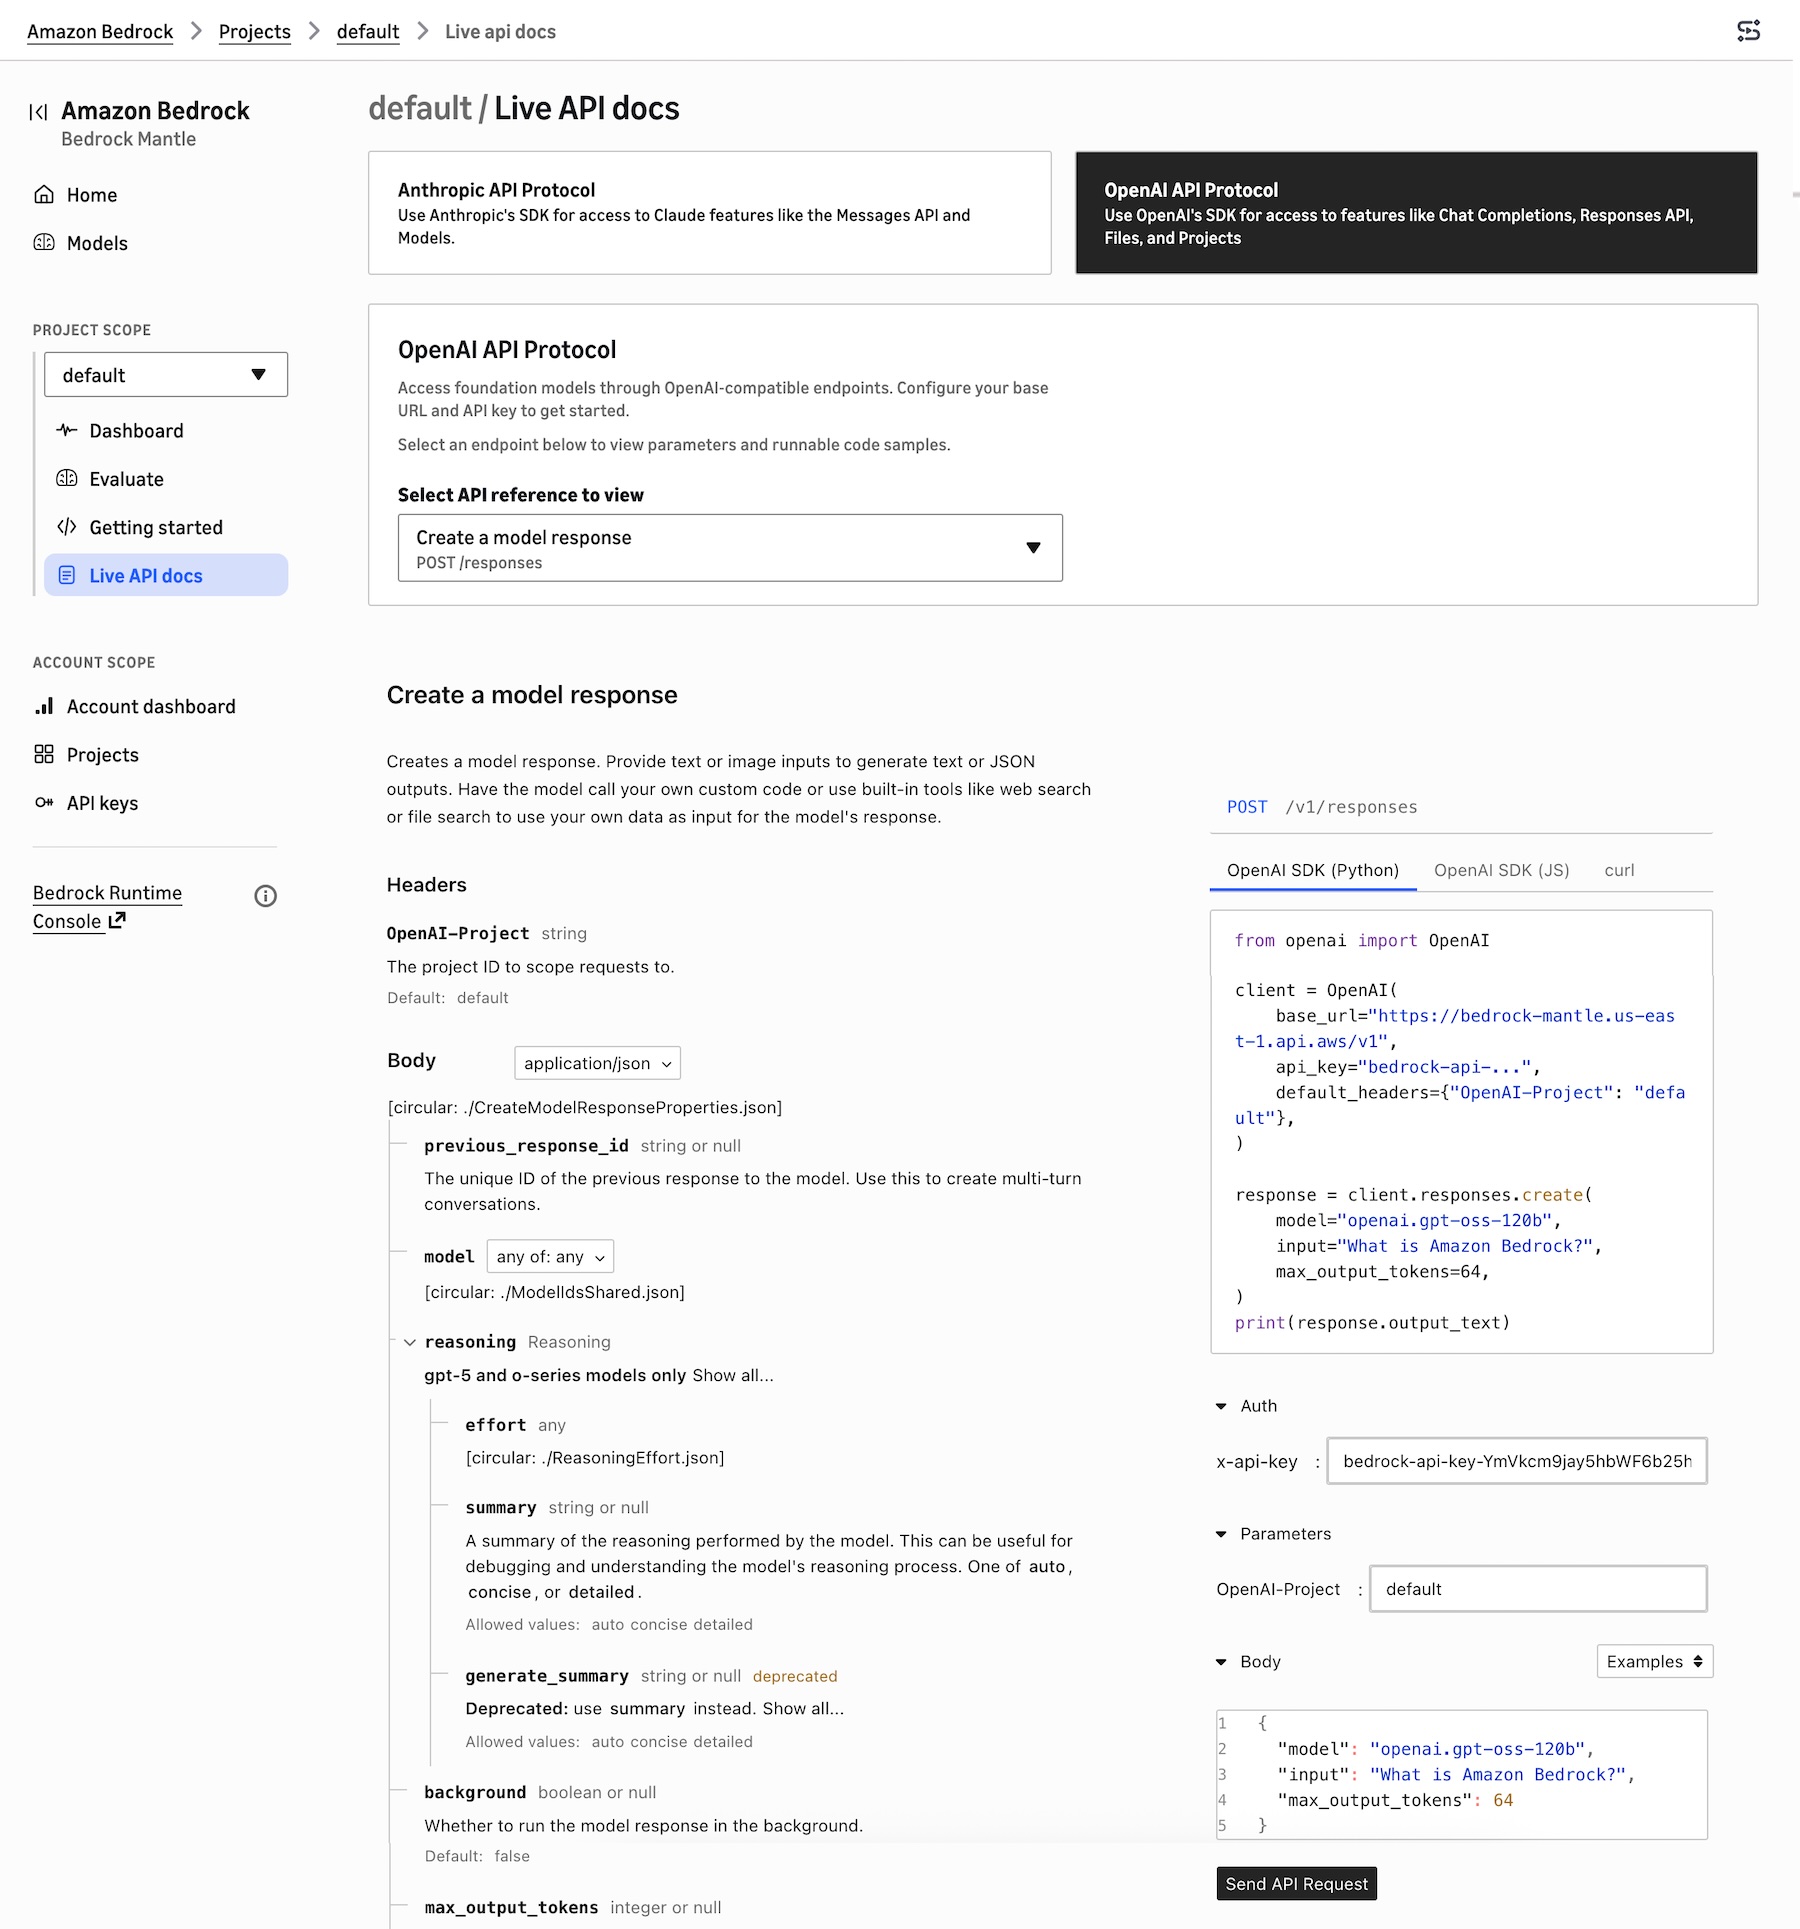
To learn about Anthropic- and OpenAI-compatible APIs, choose Live API docs. You can choose Anthropic API Protocol for access to Claude model features like the Messages API or OpenAI API Protocol for access to features like Responses API.
For example, when you choose OpenAI Response API, it retrieves a model response with the given model ID. These API references are automatically prefilled with the project’s selected model ID, Region, bedrock-mantle endpoint URL, and API key reference, and they update in place as you change models or settings.
You can also choose the existing Bedrock console to manage fully-managed features such as Agents, Knowledge Bases, Guardrails, fine-tuning, or the InvokeModel and Converse APIs to run on the bedrock-runtime endpoint.
Now available
The new console experience is available in all AWS Regions where the bedrock-mantle endpoint is offered: US East (N. Virginia, Ohio), US West (Oregon), Asia Pacific (Jakarta, Mumbai, Sydney, Tokyo), Europe (Frankfurt, Ireland, London, Milan, Stockholm), and South America (São Paulo). Check the full list of Regions for future updates.
Give the new console experience a try in the new Amazon Bedrock console and send feedback to AWS re:Post for Amazon Bedrock or through your usual AWS Support contacts.
— Channy
Post Syndicated from Sowmya Vemuri original https://aws.amazon.com/blogs/security/building-secure-b2c-applications-with-fine-grained-access-control-using-amazon-cognito-and-amazon-verified-permissions/
Modern web applications require robust security controls to protect user data and application resources. Authentication and authorization are two fundamental pillars of application security that answer critical questions: Who are you? and What are you allowed to do? Implementing these controls correctly can be challenging for developers, especially when building data-intensive applications with frameworks like Streamlit (an open-source Python framework for building interactive web applications) or when requiring fine-grained access control. Key challenges include protecting access to application resources, implementing application identity with multi-factor authentication (MFA), and implementing usage-based controls.
In this post, you will learn how to build fine-grained access controls for a sample Streamlit application using Amazon Cognito for authentication and Amazon Verified Permissions with Cedar policies for authorization. This architecture provides enterprise-grade security with minimal development effort, so you can focus on your application’s core functionality. You will learn how to reduce development time for secure applications, implement enterprise-grade authentication, through proper access management, and scale security with growing user bases.
The reference architecture follows a layered security design with four key components; separating identity verification, authorization evaluation, application logic, and enforcement boundaries. By assigning clear responsibilities to each layer, the architecture limits blast radius and ensures that a failure in any single control does not compromise the overall system.
This separation of concerns enables authentication and authorization to function as complementary security controls, following defense-in-depth principles. Figure 1 illustrates the end-to-end authentication and authorization workflow, showing how a user’s sign-in request flows through Amazon Cognito for identity verification, then through Verified Permissions for Cedar policy-based access decisions, before the application enforces the result.
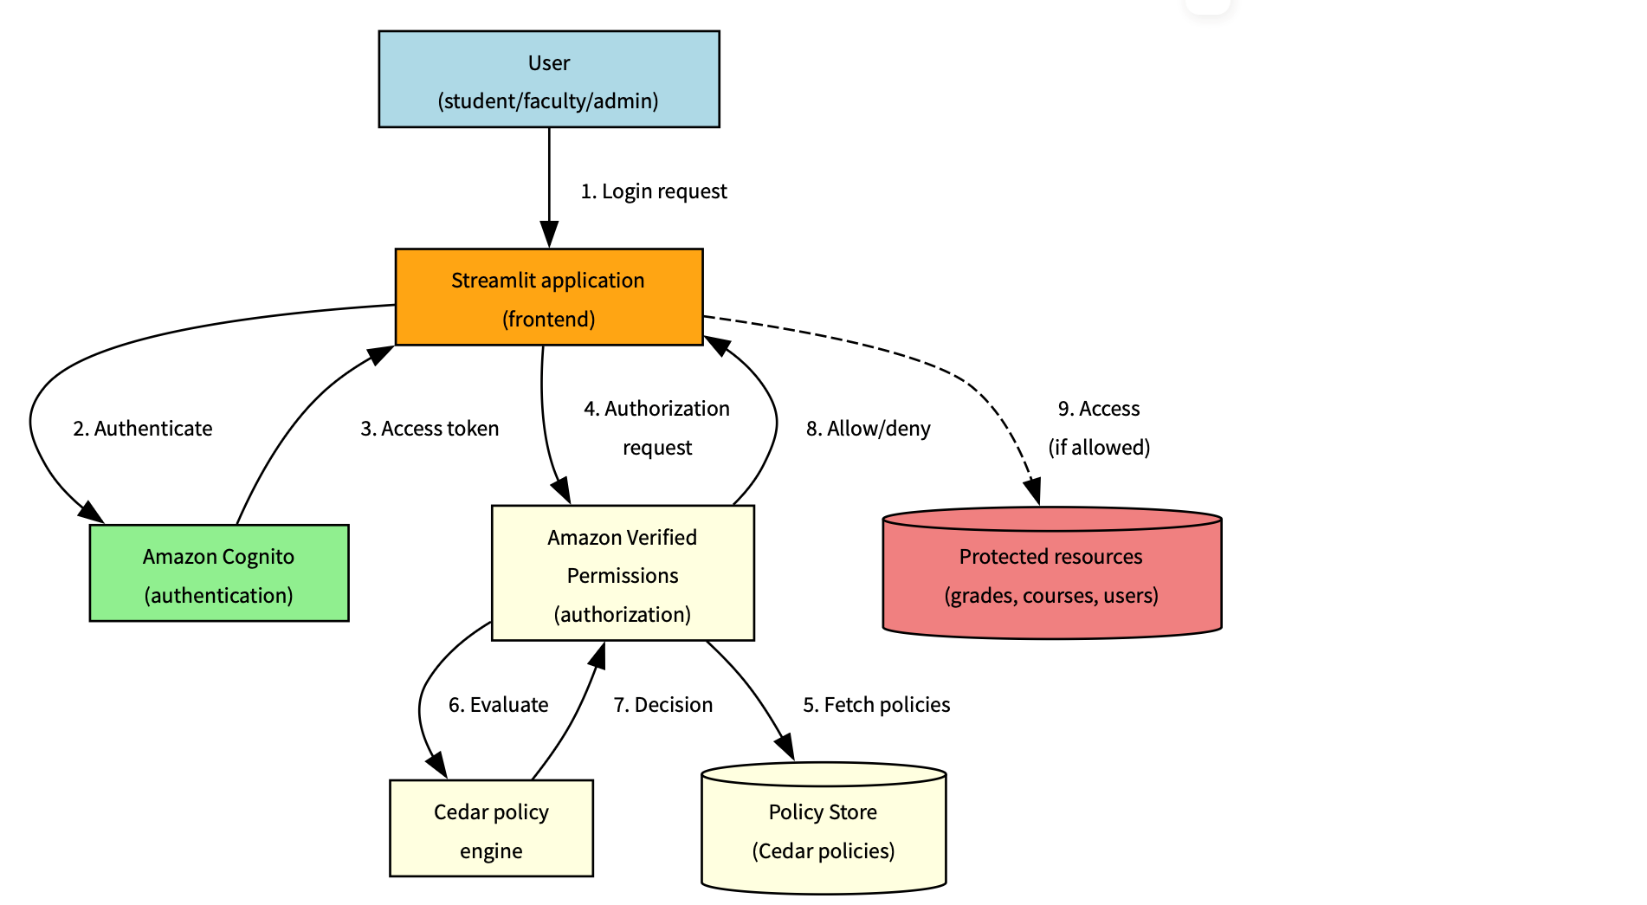
Figure 1: Solution architecture and workflow
The following workflow demonstrates how the three architecture layers work together: the authentication layer (steps 1–3) handles identity verification using Amazon Cognito, the authorization layer (steps 4–6) evaluates Cedar policies using Verified Permissions, and the application layer (steps 7–8) enforces the decision in Streamlit.
While authentication establishes user identity, authorization determines what actions users can perform. Verified Permissions provides a scalable authorization service based on Cedar, a policy language specifically designed for fine-grained access control.
Cedar policies follow a structured format that defines who can perform which actions on what resources. Let’s examine the anatomy of a Cedar policy:
Policy components
permitor forbid determines whether the policy allows or denies access?principal as a variablewhen clause contains logical expressions that must evaluate to trueThis section describes commonly used Cedar policy patterns for implementing fine-grained authorization with Amazon Verified Permissions. The examples illustrate how to model ownership, role-based access, hierarchical permissions, and administrative controls in real-world applications
This pattern helps ensure that users can only access resources they own:
What it does – This policy allows students to view only their own grades by:
Student roleentityIdThis pattern grants access based on role and resource type:
What it does – This policy allows faculty members to edit courses they teach by:
Faculty roleCourseentityIdThis pattern allows department heads to manage faculty in their department:
What it does – This policy implements departmental hierarchy controls by:
DepartmentHeadThis pattern provides emergency access with proper justification:
What it does – This policy provides emergency access capabilities by:
trueUnderstanding how policies are evaluated helps design effective authorization systems. Figure 2 shows a common evaluation pattern for an academic scenario
Note: A policy match evaluates to the policy’s effect (permit or forbid). Forbid policies take precedence: if any forbid policy matches, access is denied regardless of permit policies.
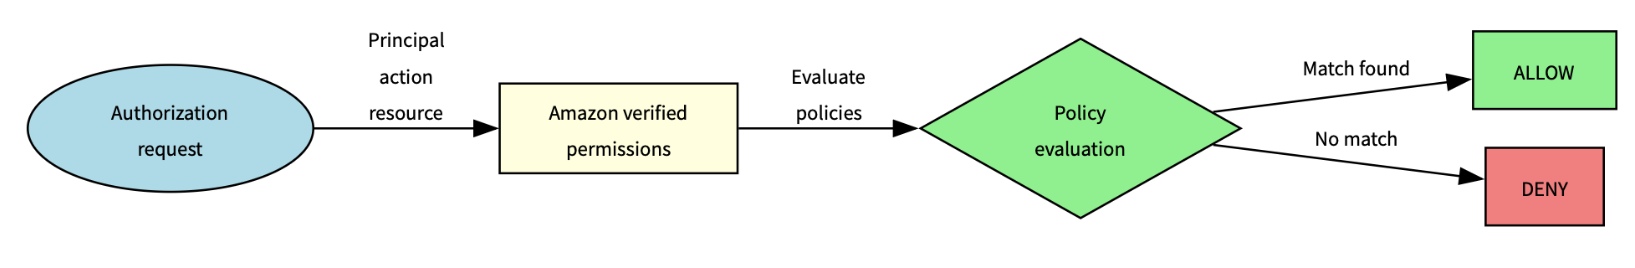
Figure 2: Policy evaluation process
The policy evaluation process follows these steps:
forbid policy matches, access is denied immediatelypermit policy matches and no forbid policies match, access is allowedALLOW or DENY) is returned to the applicationCedar is an Amazon open source policy language designed for fine-grained authorization. Every policy defines who (principal) can perform what action on which resource under what conditions, as shown in Figure 3.
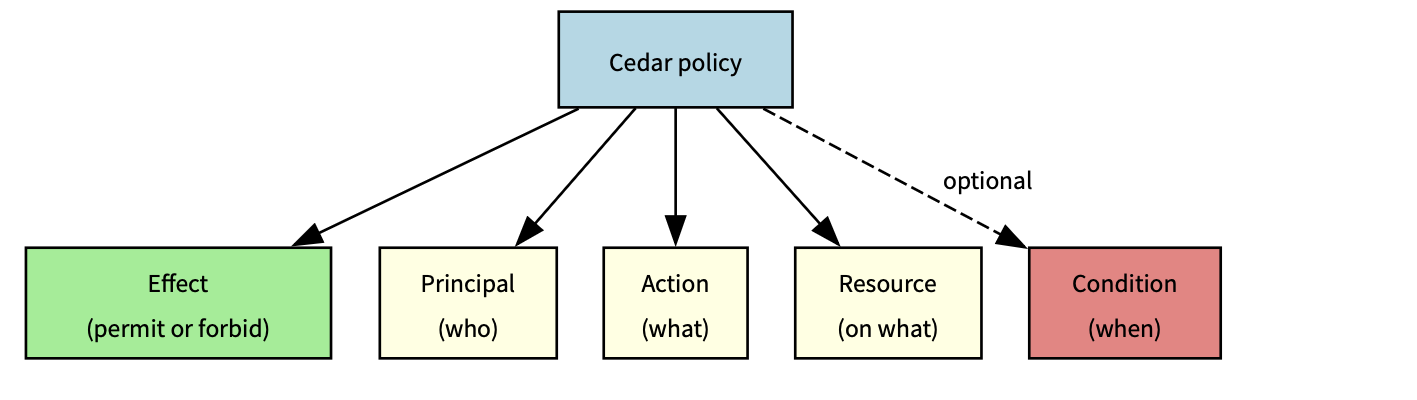
Figure 3: Cedar policy definitions
The following table shows how different policies interact in complex scenarios where multiple policies could apply:
| Scenario | Student policy | Faculty policy | Department head policy | Admin policy |
| Student accessing own grade | Permit | N/A | N/A | Override |
| Faculty editing course | N/A | Permit | N/A | Override |
| Department head managing faculty | N/A | N/A | Permit | Override |
| Emergency admin access | N/A | N/A | N/A | Permit |
Legend:
The preceding table shows how each role’s policy applies to different scenarios, with admin access having override capabilities across most situations except for emergency admin access where it’s the primary permit authority. The Override column specifically indicates that the administrator’s emergency access policy can supersede other role-specific policies, but only when the emergencyAccess context flag is explicitly set and a justification is provided. This is not an automatic override.
Policy optimization tips:
entityId, role, resource type) as primary conditions. Best practices for designing an authorization modelConsider an academic system with different user roles and their corresponding permissions:
Student: View own grades
Faculty: Edit course content, manage grades
Teaching assistant (TA): Grade management and course support
Department head: Manage faculty assignments
Administrator: System-wide access
To implement the preceding Academic system application, you need an active AWS account, Python 3.8 or later, basic Streamlit knowledge, and AWS Identity and Access Management (IAM) permissions for Amazon Cognito and Verified Permissions.
This provisions an Amazon Cognito user pool, a Verified Permissions policy store, and any sample resources needed for the demo.
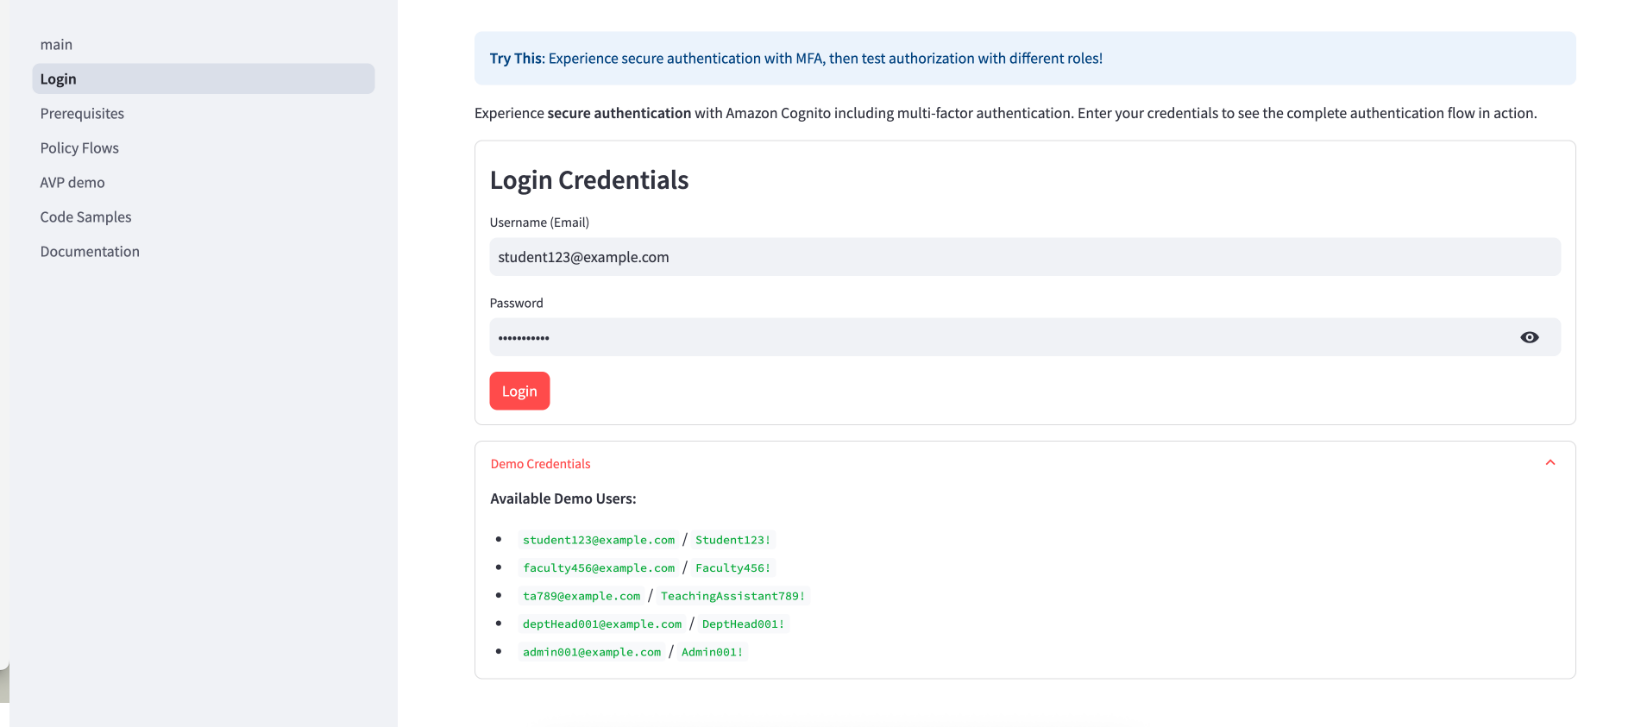
Figure 4: Verify login credentials
Ctrl+C to shut down and stop.When implementing this architecture, follow these best practices to support security:
Implementing proper authentication and authorization is critical for application security. By using Amazon Cognito and Amazon Verified Permissions, you can build robust security controls without complex custom code. Through this approach, you can implement enterprise-grade authentication with minimal effort, define and enforce fine-grained authorization policies, scale your security controls as your application grows, and centrally manage and audit security policies.
To get started with your implementation, create your AWS resources including an Amazon Cognito user pool and Verified Permissions policy store. Define your Cedar policies based on your application’s access requirements. Integrate authentication and authorization checks into your application flow. Test thoroughly with different user roles and access scenarios. Finally, monitor and refine your security controls based on usage patterns.
For additional resources, check out the Amazon Cognito documentation and Amazon Verified Permissions documentation.
If you have feedback about this post, submit comments in the Comments section below.
Post Syndicated from Brendan Watters original https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-05-06-2026
Several fun modules landed this week, including an Apache RCE, Windows Kernel pointer collection, and Gogs RCE via naming. Leading off is Gogs’ RCE that allows an attacker to execute commands by naming their branch –exec <command> and requesting a rebase.
Another useful post module by CharlesQuinnDev enumerates the Kernel pointers leaked via the popular NtQuerySystemInformation technique. Those exposed pointers, combined with a good write primitive, make local privilege escalation easier to accomplish. Several local privilege escalations already use that technique, so exposing just that technique was a great call!
Authors: dinosn and h00die
Type: Exploit
Pull request: #21497 contributed by h00die
Path: multi/http/apache_activemq_jolokia_rce
AttackerKB reference: CVE-2026-34197
Adds a new exploit module exploit/multi/http/apache_activemq_jolokia_rce targeting CVE-2026-34197 in Apache ActiveMQ. The module abuses the Jolokia JMX-over-HTTP API exposed at /api/jolokia/ by calling the addNetworkConnector() MBean operation with a crafted brokerConfig=xbean:http://… URI. ActiveMQ fetches the attacker-controlled URL and instantiates it as a Spring XML application context, achieving remote code execution via a java.lang.ProcessBuilder bean. Authentication is required to exploit this vulnerability.
Author: Crypto-Cat
Type: Exploit
Pull request: #21515 contributed by jburgess-r7
Path: multi/http/gogs_rebase_rce
This adds an exploit module for the Gogs rebase Remote Code Execution (RCE) vulnerability. The module leverages an argument injection flaw residing in the pull request merge workflow of Gogs versions <= 0.14.2 and <= 0.15.0+dev.
Author: CharlesQuinnDev
Type: Post
Pull request: #21039 contributed by CharlesQuinnDev
Path: windows/gather/windows_kernel_pointer_enum
Adds a new post module for Windows that enumerates kernel object pointers exposed through NtQuerySystemInformation on x64 systems. The module collects observable handle metadata and provides analysis of pointer distribution, object types, and ALPC usage, then saves the results to a CSV loot file for review. Also introduces a reusable Windows kernel handle-enumeration library.
You can find the latest Metasploit documentation on our docsite at docs.metasploit.com.
As always, you can update to the latest Metasploit Framework with msfupdate and you can get more details on the changes since the last blog post from GitHub:
If you are a git user, you can clone the Metasploit Framework repo (master branch) for the latest. To install fresh without using git, you can use the open-source-only Nightly Installers or the commercial edition Metasploit Pro.
Post Syndicated from Matt Granger original https://www.youtube.com/shorts/T-f5Lo2oM4M
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=iTYVBNQbEkU
Post Syndicated from Ryan Smith original https://www.servethehome.com/scoping-out-rtx-spark-sff-mini-pcs-at-computex-2026/
While at Computex, we caught a look at some of the upcoming SFF mini-PCs based on NVIDIA’s RTX Spark SoC, including systems from ASUS, Dell, Lenovo, and MSI
The post Scoping Out RTX Spark SFF Mini-PCs at Computex 2026 appeared first on ServeTheHome.
Post Syndicated from Rommel Sunga original https://aws.amazon.com/blogs/messaging-and-targeting/adding-line-messenger-to-your-aws-omnichannel-fallback-solution/
In this post, you will learn how to extend an existing omnichannel fallback solution by integrating LINE Messenger, including architecture updates, deployment steps, and testing procedures. The original solution, built with Amazon API Gateway, AWS Lambda, Amazon Simple Email Service (Amazon SES), and AWS End User Messaging, delivers messages across SMS, WhatsApp, and email with automatic fallback capabilities.
For more information about the original omnichannel fallback solution that this aims to extend to LINE, see the Enhancing Message Reach: An Omnichannel Approach Using WhatsApp, SMS, and Email with AWS.
LINE is a popular messaging platform in Japan, Taiwan, and Thailand, with 181 million monthly active users across its primary markets, including 100 million in Japan alone (LY Corporation FY2025 Q3 earnings data). With an 84 percent DAU/MAU ratio (88 percent in Japan), LINE sees high daily engagement, making it a reliable channel for time-sensitive communications such as appointment reminders in healthcare, order and shipping notifications in ecommerce, and promotional campaigns in retail.
While other messaging platforms are popular in specific APAC markets (KakaoTalk in South Korea, WeChat in China, Zalo in Vietnam, Viber in the Philippines), LINE holds a strong position across Japan, Taiwan, and Thailand simultaneously, making it a high-impact addition to a multi-channel messaging strategy for those countries. By adding LINE to the omnichannel fallback solution, you can reach your audience on their preferred messaging channel in these key markets. You can use LINE as either a primary or fallback channel while maintaining the same fallback and broadcast patterns already available for other channels.
Cost note: LINE Messaging API pricing varies by country and plan. See the pricing pages for LINE Messaging API, Amazon Simple Email Service (Amazon SES), and Amazon End User Messaging for details on each channel.
Adding LINE to your fallback solution means you can now cover four major messaging channels from a single API endpoint, giving you broader reach without added operational complexity. The LINE integration follows the same event-driven serverless pattern as the existing channels. The following diagram shows the key additions to the architecture.
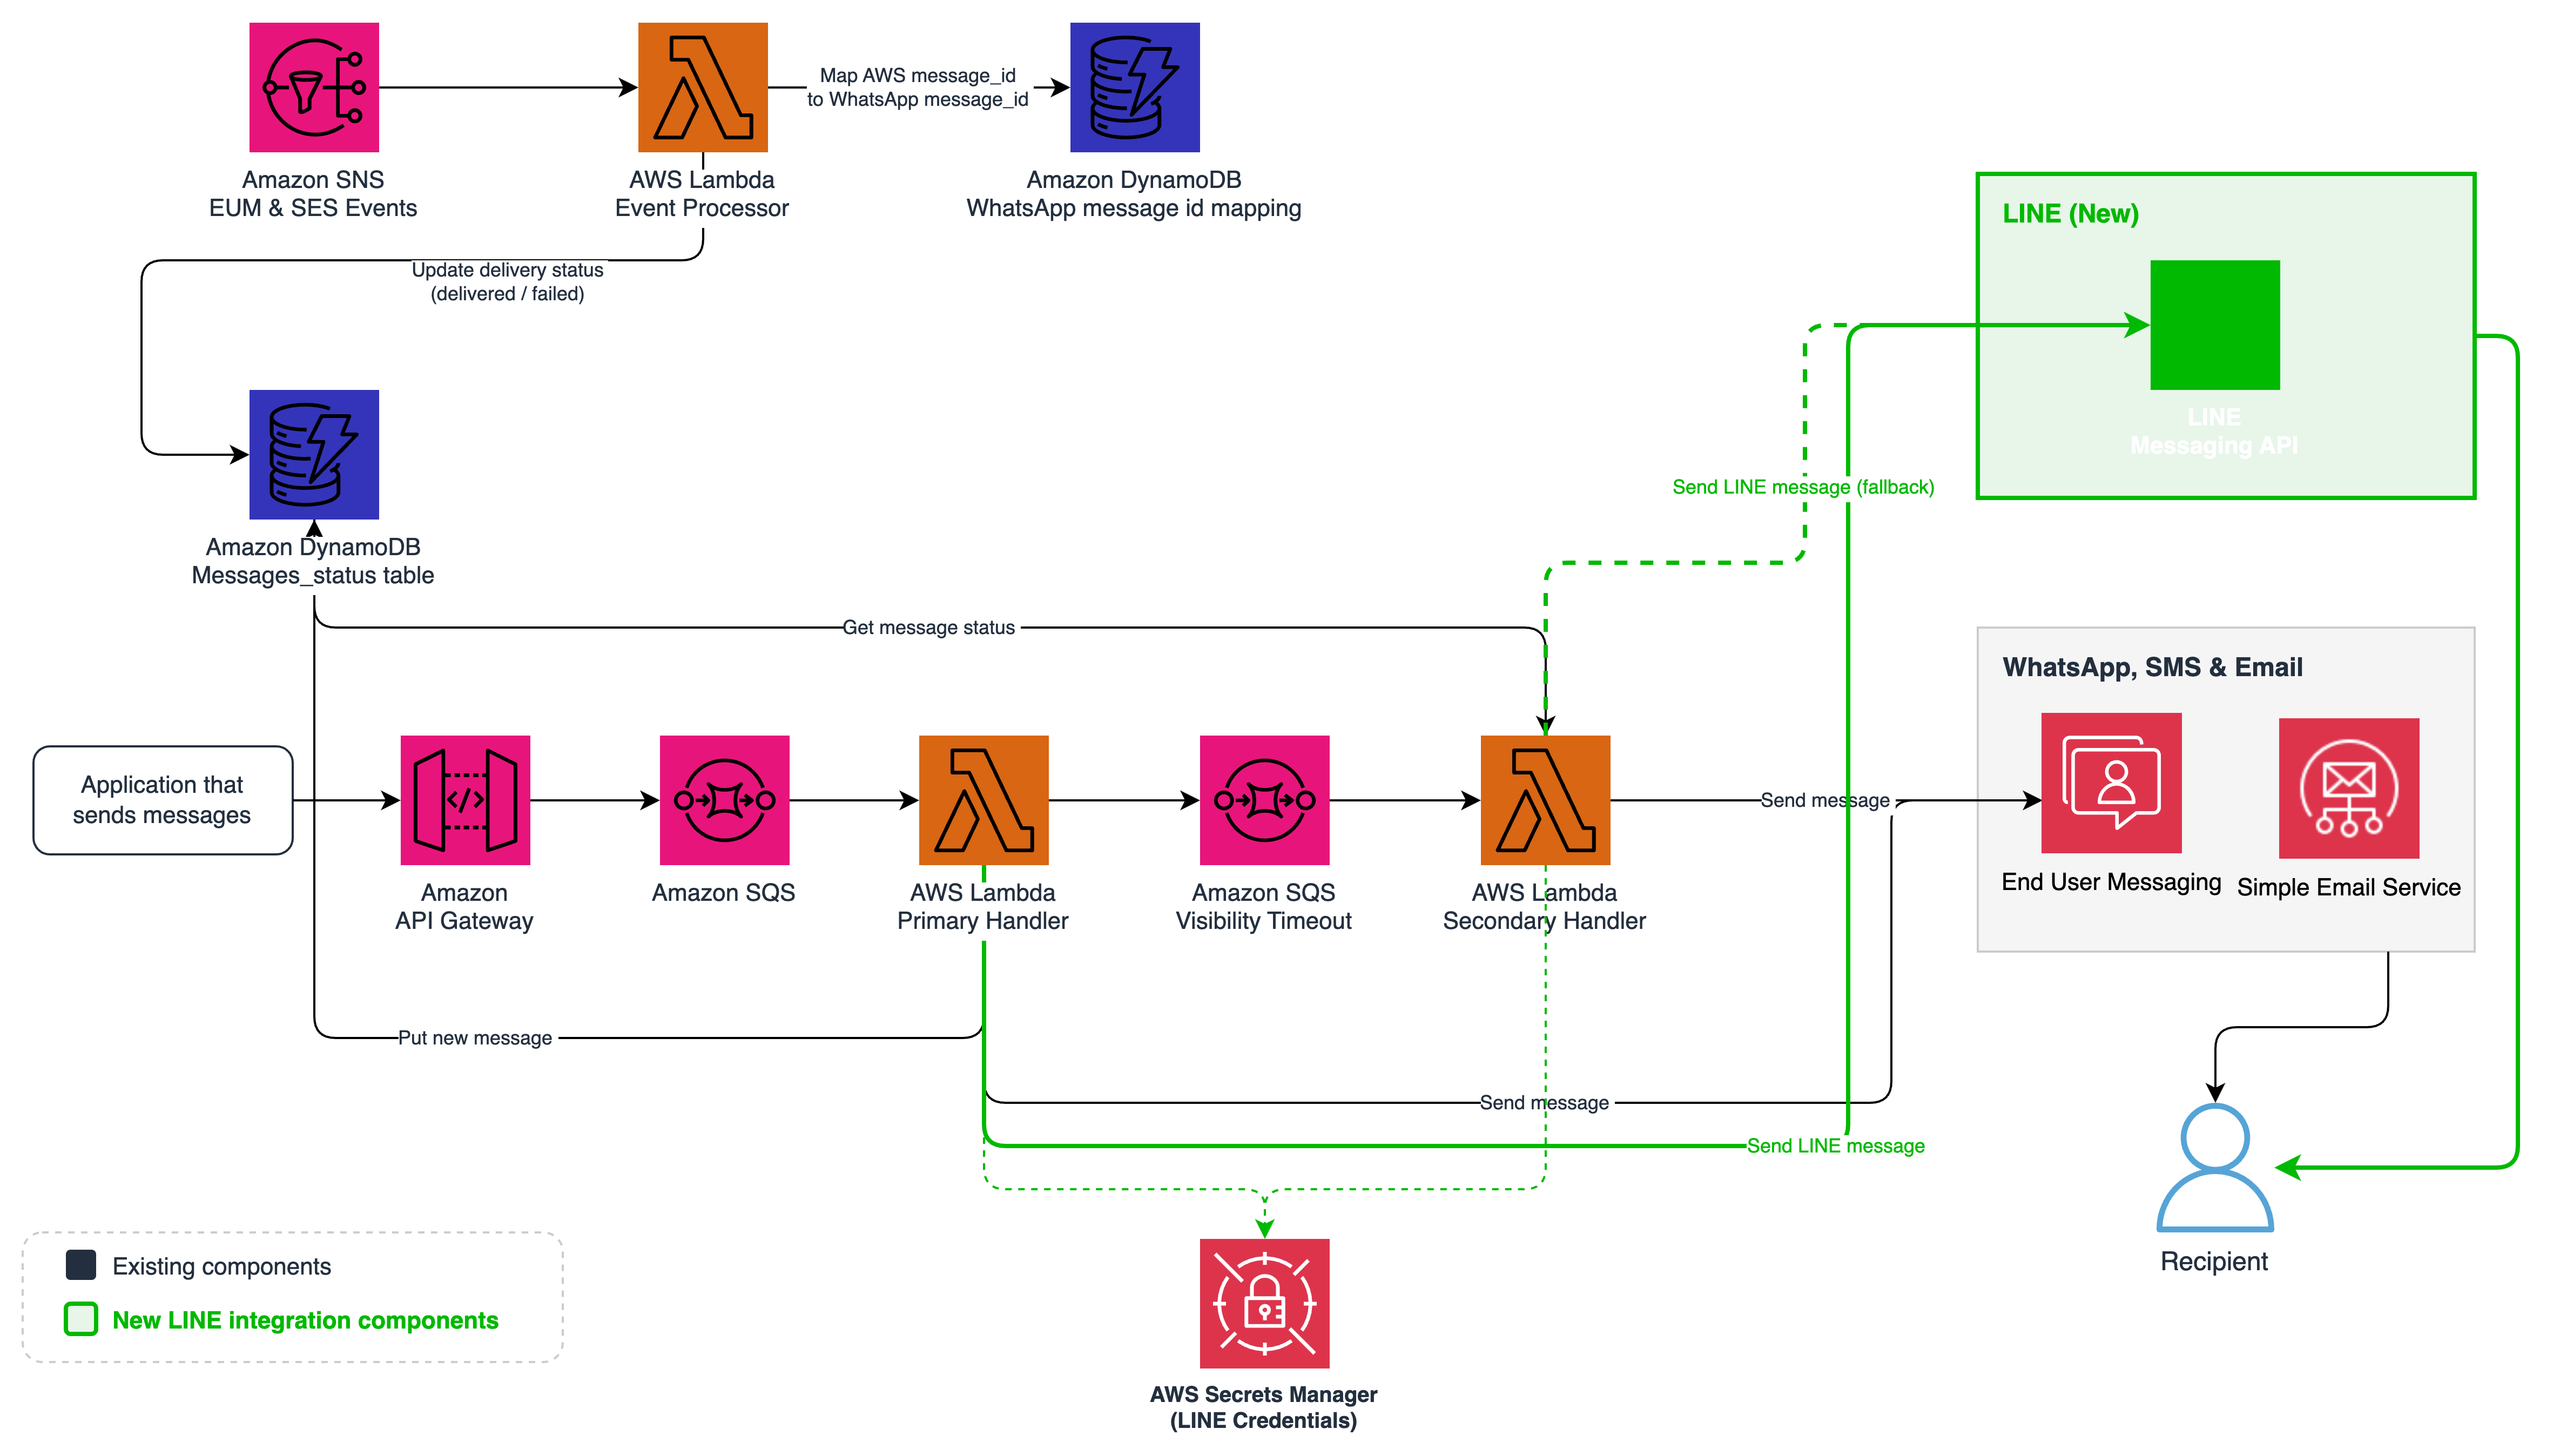
Figure 1: Updated omnichannel architecture with LINE Messenger (new components highlighted)
You can now reach LINE users with two straightforward additions to the existing architecture:
LINE Messaging API Integration – The Primary and Secondary Handler Lambda functions now include a send_line module that calls the LINE Messaging API to deliver messages using the Push Message endpoint.
AWS Secrets Manager Integration – LINE channel credentials (access token and channel secret) are stored securely in AWS Secrets Manager and retrieved by Lambda functions with caching for performance.
The LINE Messenger integration extends the existing message processing pipeline, so you get the same reliable fallback behavior that you already have for email, SMS, and WhatsApp. The following sections describe how the system handles LINE messages and fallback scenarios.
When you send a message with LINE as the primary or fallback channel, the flow follows the same pattern as other channels with LINE-specific handling:
| Aspect | SMS | LINE | ||
| API | Amazon SES SendEmail API | AWS End User Messaging SendTextMessage API | AWS End User Messaging Social SendWhatsAppMessage API | LINE Messaging API Push Message API |
| Authentication | IAM roles | IAM roles | IAM roles | Channel access token via Secrets Manager |
| External Message ID Mapping | Not required. SES returns the same message ID in delivery callbacks | Not required. SMS returns the same message ID in delivery callbacks. | Required. WhatsApp returns a different platform message ID in delivery webhooks that must be mapped back to the internal AWS message ID. | Not required. No delivery callbacks exist, so no message ID correlation is needed. |
| Credential Storage | IAM (automatic) | IAM (automatic) | IAM (automatic) | Secrets Manager (manual) |
| Delivery Tracking | Async via SES delivery events (SNS callback updates DynamoDB) | Async via End User Messaging events (SNS callback updates DynamoDB) | Async via End User Messaging events (SNS callback updates DynamoDB) | None. Status set to delivered immediately on 200 response from LINE API. No delivery webhook available for LINE Messaging API. |
LINE uses an external API with its own authentication rather than AWS-native IAM authentication. This means you must manage credentials through AWS Secrets Manager rather than relying on AWS Identity and Access Management (IAM)-managed authentication. For more information, see the LINE Messaging API documentation.
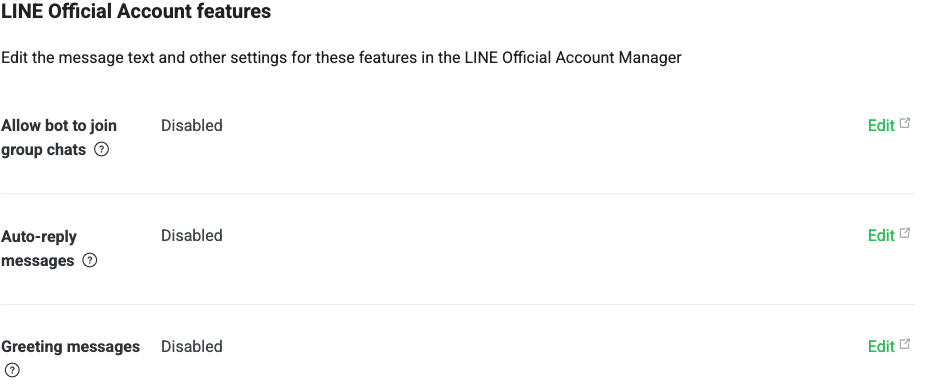
LINE offers two distinct messaging products for businesses, LINE Messaging API, and LINE Official Notification.
You need a LINE Messaging API Channel to authenticate and send messages through the LINE integration. The following steps walk you through creating one:
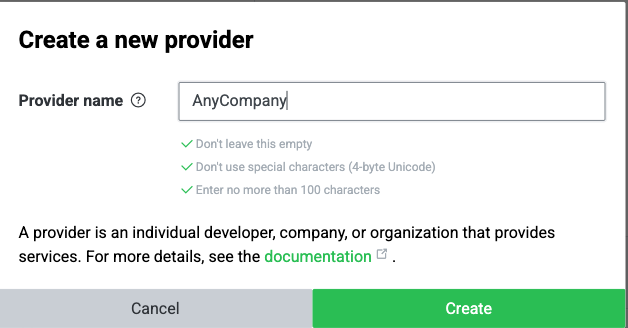
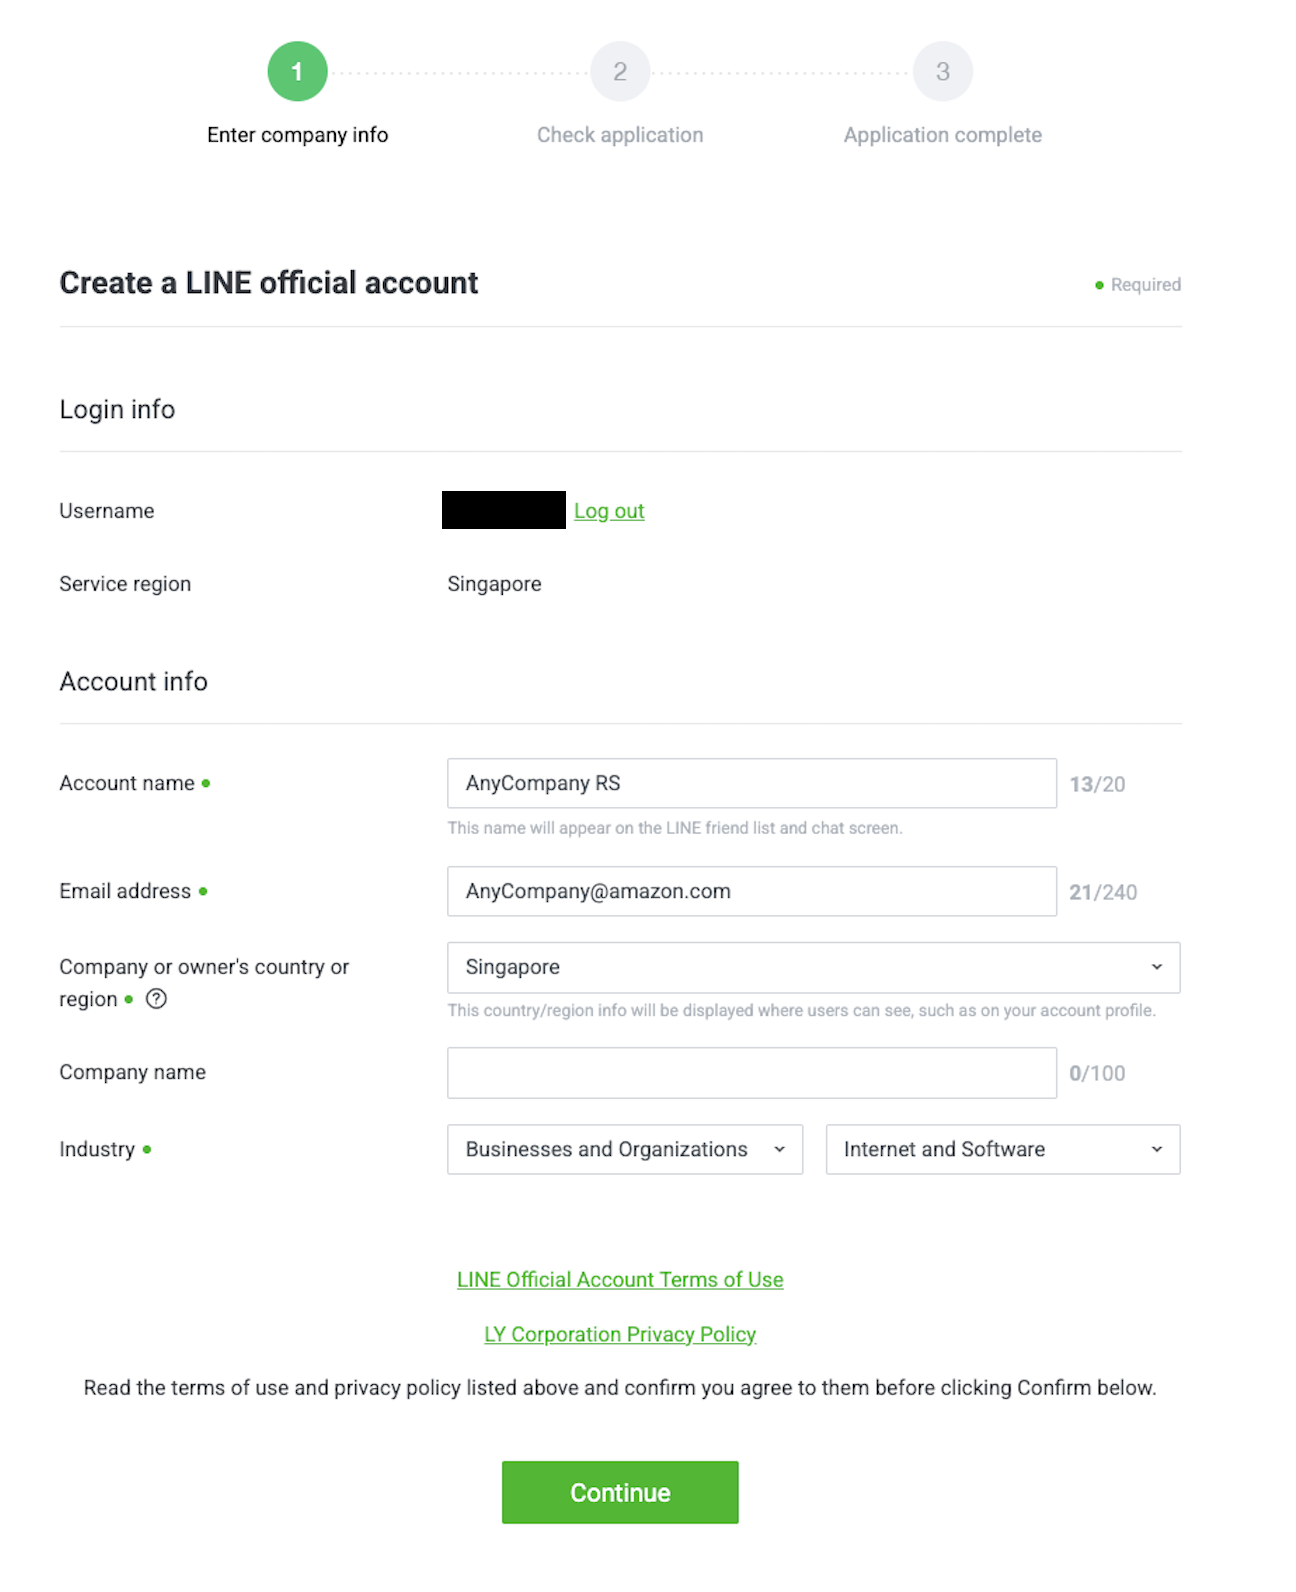
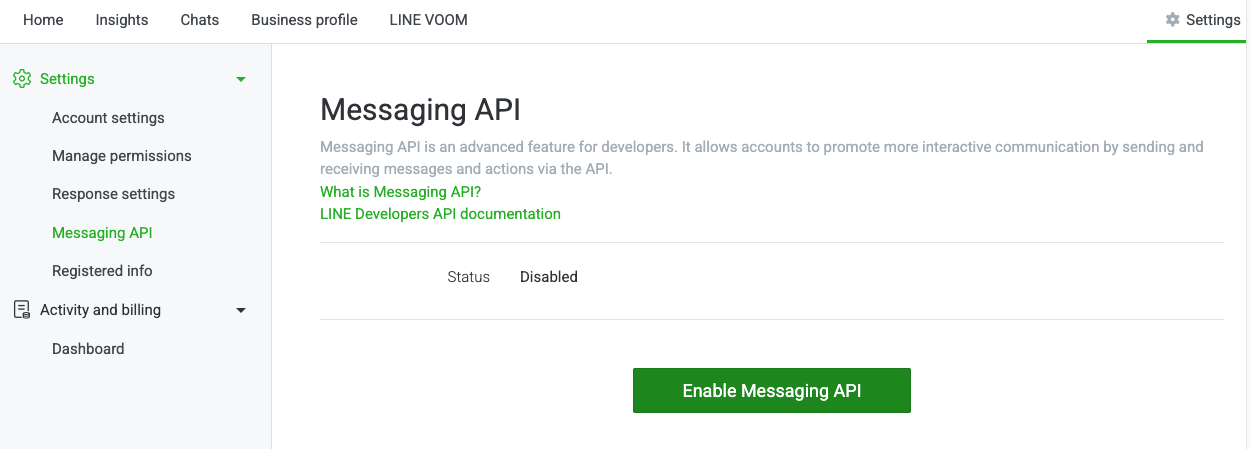
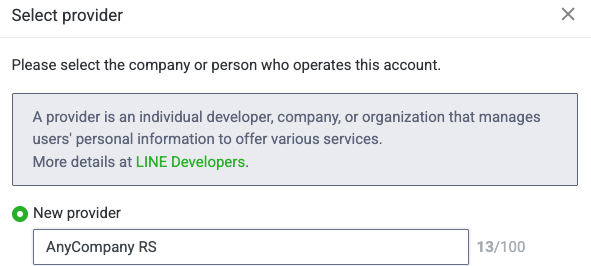
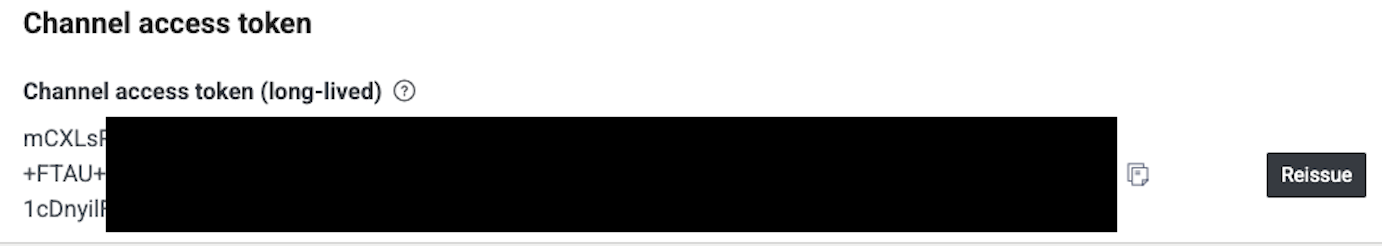
The repository includes a complete deployment guide with step-by-step instructions for deploying the CDK stack, configuring LINE credentials in AWS Secrets Manager, obtaining personal LINE user IDs, and running the integration test suite. The test suite automatically detects which channels are configured and runs the applicable tests. For full deployment and testing instructions, see the Deployment Guide in the repository.
Before deploying this solution to production, review the following considerations and adjust for your workload and compliance obligations.
The Lambda execution roles in the sample scope DynamoDB, Amazon SQS, and AWS Secrets Manager permissions to specific resource ARNs. The send actions for Amazon SES (ses:SendEmail, ses:SendTemplatedEmail), SMS (sms-voice:SendTextMessage), and WhatsApp (social-messaging:SendWhatsAppMessage) are granted on resources: [“*”] in this sample for simplicity, because the specific sending identities, phone pools, and WhatsApp business accounts are left configurable. For production, scope these further where the API supports it: SES allows identity-level ARNs (for example, arn:aws:ses:region:account:identity/example.com), and End User Messaging SMS supports pool and phone-number ARNs. When adapting this code, keep resource-level scoping for everything that supports it and review the AWS Well-Architected Security Pillar and Lambda execution role guidance for production deployments.
LINE channel access tokens are long-lived and are issued and rotated manually through the LINE Developers Console; there’s no programmatic rotation API. Rotate the token periodically in line with your organization’s key-rotation policy (for example, every 90 days), update the Secrets Manager secret with the new value, and force a Lambda cold start (by redeploying the stack or updating a Lambda environment variable) so the cached credentials are refreshed.
The solution stores message metadata and recipient identifiers (including LINE User IDs, phone numbers, and email addresses) in Amazon DynamoDB. DynamoDB uses AWS-managed encryption at rest, Secrets Manager uses AWS Key Management Service (AWS KMS), and all outbound calls to the LINE API are made over HTTPS. Point-in-time recovery is enabled on the message table.
The sample doesn’t configure a DynamoDB Time-to-Live (TTL) attribute, so records persist indefinitely. For production, add a TTL attribute (for example, expiresAt) that matches your retention policy, and review whether the RemovalPolicy.RETAIN setting on the tables is appropriate for your environment. LINE User IDs, phone numbers, and email addresses are personally identifiable information under regulations including Japan’s APPI, the EU’s GDPR, and similar laws. Assess your retention obligations, data residency requirements, and processes for handling subject access and deletion requests for the regions you serve.
By adding LINE Messenger to the omnichannel fallback solution, you can now reach your customers across the four messaging channels that matter most: email, SMS, WhatsApp, and LINE. The integration follows the same serverless, event-driven patterns as the existing channels, making it straightforward to deploy and maintain. LINE can serve as either a primary or fallback channel, giving you the flexibility to tailor your messaging strategy to regional preferences. As a next step, consider adding other regional messaging services to further expand your reach. You can also explore advanced LINE features such as rich messages, quick replies, and Flex Messages to create more engaging customer interactions.
Post Syndicated from Rommel Sunga original https://aws.amazon.com/blogs/messaging-and-targeting/send-whatsapp-business-messages-with-aws-end-user-messaging-social/
WhatsApp reaches over 3 billion monthly active users worldwide — with more than 2 billion using it every day — making it the single most direct channel for customer communication at global scale. AWS End User Messaging Social gives you a managed API to send WhatsApp Business messages without building or maintaining your own WhatsApp Business API integration.
Whether you’re building appointment reminders, order notifications, or interactive customer support flows, with WhatsApp Business messaging, you can meet customers where they already communicate.
This post is for developers and solutions architects looking to integrate WhatsApp messaging into their customer engagement workflows using AWS. By the end, you will know how to send every supported message type—from straightforward text and media to templates, interactive menus, and WhatsApp Flows—using Python and the AWS End User Messaging Social API.
This solution uses AWS End User Messaging Social to connect your WhatsApp Business Account (WABA) with your AWS workloads, enabling automated, two-way messaging with your customers. When a customer sends a WhatsApp message to your WABA phone number, AWS End User Messaging Social receives the message and publishes an event to an Amazon Simple Notification Service (Amazon SNS) topic. Amazon SNS then invokes an AWS Lambda function. You configure this Lambda function to process the incoming message and send a contextual WhatsApp reply to the customer. The following diagram illustrates this architecture:
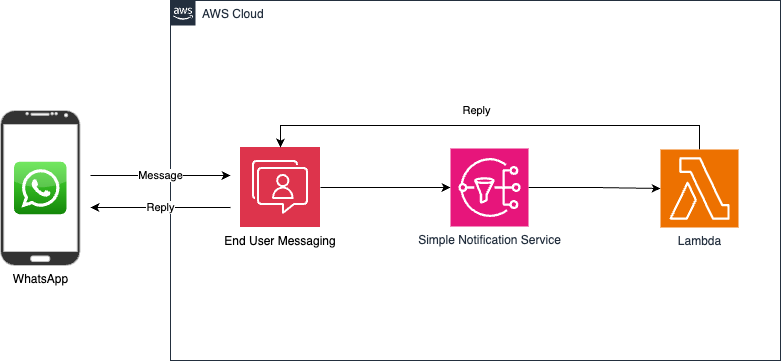
Figure A: Shows the architecture flow “Customer WhatsApp → End User Messaging Social → SNS → Lambda → End User Messaging Social → Response”
IMPORTANT: Note that any WhatsApp user can send a message to your WABA number and trigger the workflow. To avoid incurring ongoing charges, complete the steps in the “Clean up” section.
The solution is deployed using the AWS Serverless Application Model (AWS SAM) and includes a sample Lambda function that demonstrates how to handle common message types, send interactive list messages, and respond with templated replies. You can extend this foundation to build more sophisticated workflows, such as invoking AWS Step Functions for multi-step processes or routing messages to container-based workloads running on AWS. AWS End User Messaging Social also provides unified billing within AWS, streamlining cost management for your WhatsApp messaging workloads.
Before you run any of the examples in this post, complete the following prerequisites:
This walkthrough typically takes 30–45 minutes, though actual time might vary based on your familiarity with AWS services and WhatsApp Business configuration.
If you’re new to AWS End User Messaging Social, see the Getting Started with WhatsApp guide before proceeding.
To configure AWS End User Messaging Social, you will need several types of permissions depending on what you’re setting up. Here are the key permissions required:
For basic configuration and management, you will need permissions for the following actions:
social-messaging:AssociateWhatsAppBusinessAccount — to associate a WhatsApp Business Account with your AWS accountsocial-messaging:CreateWhatsAppMessageTemplate — to create WhatsApp message templatessocial-messaging:ListLinkedWhatsAppBusinessAccounts — to list linked WhatsApp Business Accountssocial-messaging:GetWhatsAppMessageTemplate — to retrieve message template detailssocial-messaging:ListWhatsAppMessageTemplates — to list message templatesIf you’re configuring event destinations with Amazon SNS, your SNS topic must have a resource policy allowing the sms-voice.amazonaws.com service principal to publish to it, and you will need an AWS Identity and Access Management (IAM) role with a trust policy allowing social-messaging.amazonaws.com to assume it. For detailed setup instructions, see Configuring Event Destinations in the AWS End User Messaging Social User Guide.
If integrating with Amazon Connect, the service-linked role (SLR) includes the following permissions:
social-messaging:SendWhatsAppMessagesocial-messaging:PostWhatsAppMessageMediasocial-messaging:GetWhatsAppMessageMediasocial-messaging:GetLinkedWhatsAppBusinessAccountPhoneNumberFor more information, see Amazon Connect Service-Linked Role in the Amazon Connect Administrator Guide.
Create a config.json file in your project directory with the following structure to store the destination WhatsApp number and the origination phone number ID (for example, phone-number-id-a1b2c3d4######) that we’re sending messages from and receiving the message:
Security note: The config.json file is intended for local testing only. In production environments, avoid hardcoding phone numbers and credentials. Instead, use AWS Secrets Manager, AWS Systems Manager Parameter Store, or environment variables to manage sensitive configuration values.
Each example builds a message_data payload and sends it using the following code:
For production use, wrap the send call with error handling to manage throttling and failures gracefully:
The following sections show only the message_data for each message type. To send any of these messages, use the shared sending code from the previous Configuration section—load config.json, create the Boto3 client, and call client.send_whatsapp_message() with the payload.
Text messages are plain text communications sent within the 24-hour conversation window. They don’t require Meta template approval and support basic formatting.
Text messages are the foundation of WhatsApp conversations. You can send up to 4,096 characters per message. Text messages don’t require Meta approval and work within an active 24-hour conversation window that opens when a customer messages your business first, or when you initiate contact using an approved template.
The following image is a WhatsApp message example.

The following is a code example for the previous message.
With Media messages, you can send images, documents, audio, and video files.
Note: Media uploaded to Meta is retained for 30 days. If you reuse media across messages (such as a company logo), use the external URL method or re-upload before sending. The examples in this post use external URLs.
The message is presented as a PDF with the provided message body in the following example.
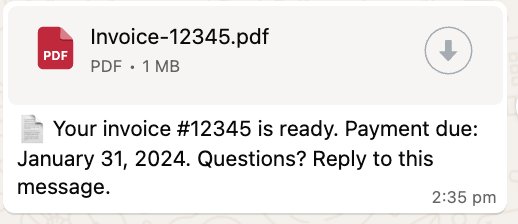
The following is a code example for the previous message.
This media message includes an image with a message body in the following example to describe the image. In this case it shows a laptop available for purchase with a link included as part of the message body.
The following is a code example for the previous message.
Template messages enable business-initiated conversations outside the 24-hour window. Templates must be created and approved by Meta before use.
Template creation using CLI
While it’s possible to create templates directly in the AWS End User Messaging Social console and in WhatsApp Manager’s UI, you can also use AWS End User Messaging Social to programmatically create templates using the AWS CLI.
Step 1 — Create a file named order_confirmation_template.json in your working directory with the following template definition.
Step 2 — Run the following CLI command to create the template. Note that the –template-definition parameter points to the local JSON file that contains the template structure:
Template creation using the console
AWS End User Messaging Social also features a built-in template management UI which you can use to create and manage templates directly within the AWS End User Messaging Social portion of the AWS Console under AWS End User messaging > Social Messaging > Message Templates. To create a new template, choose the Create Template button.
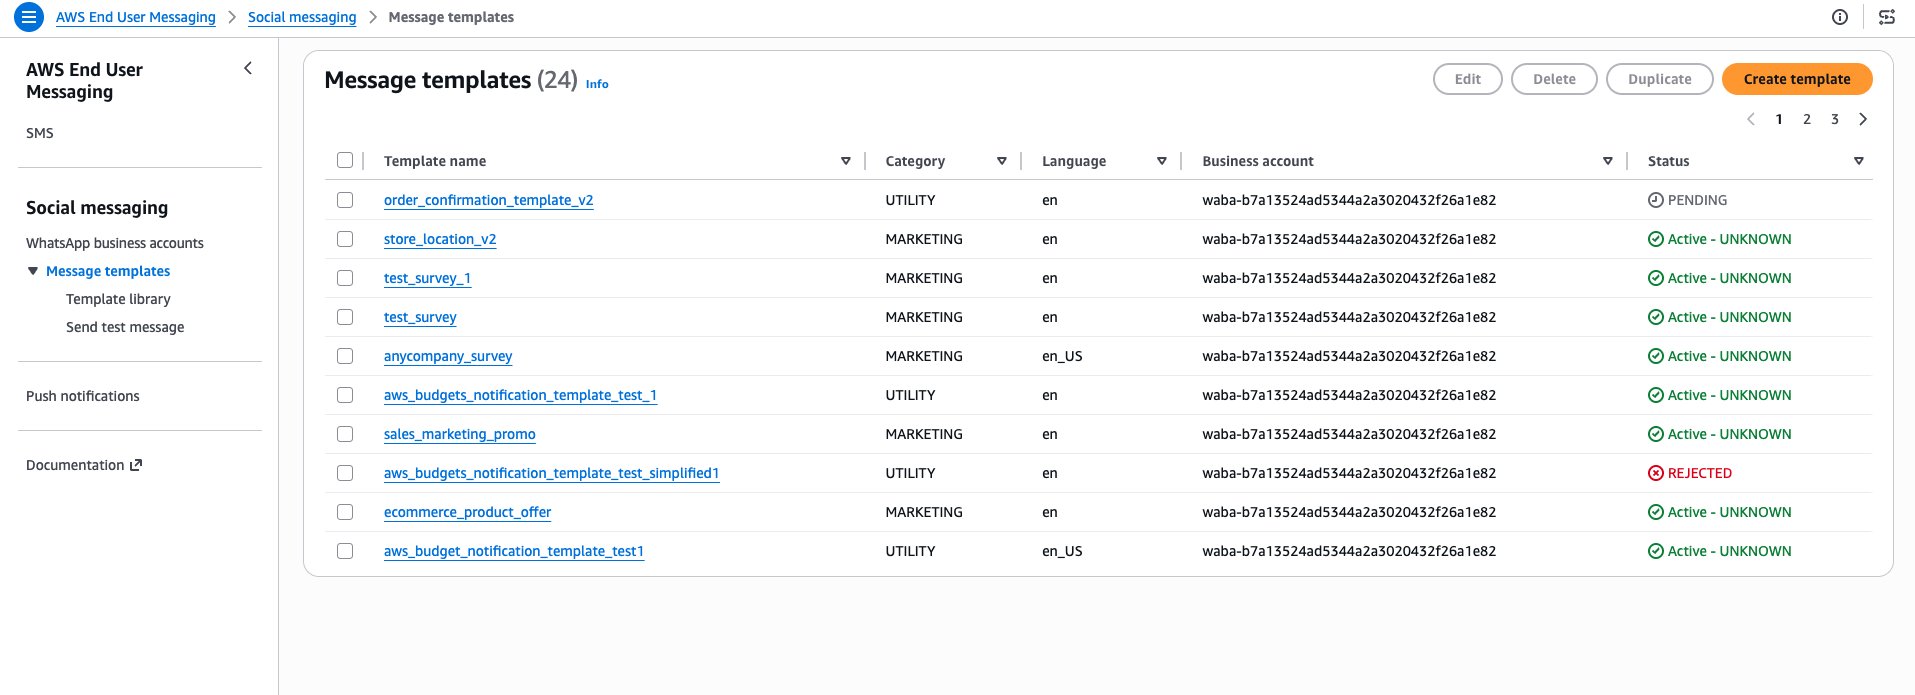
In the first screen, you can set your template name, template language and template type for your respective WhatsApp Business Account.
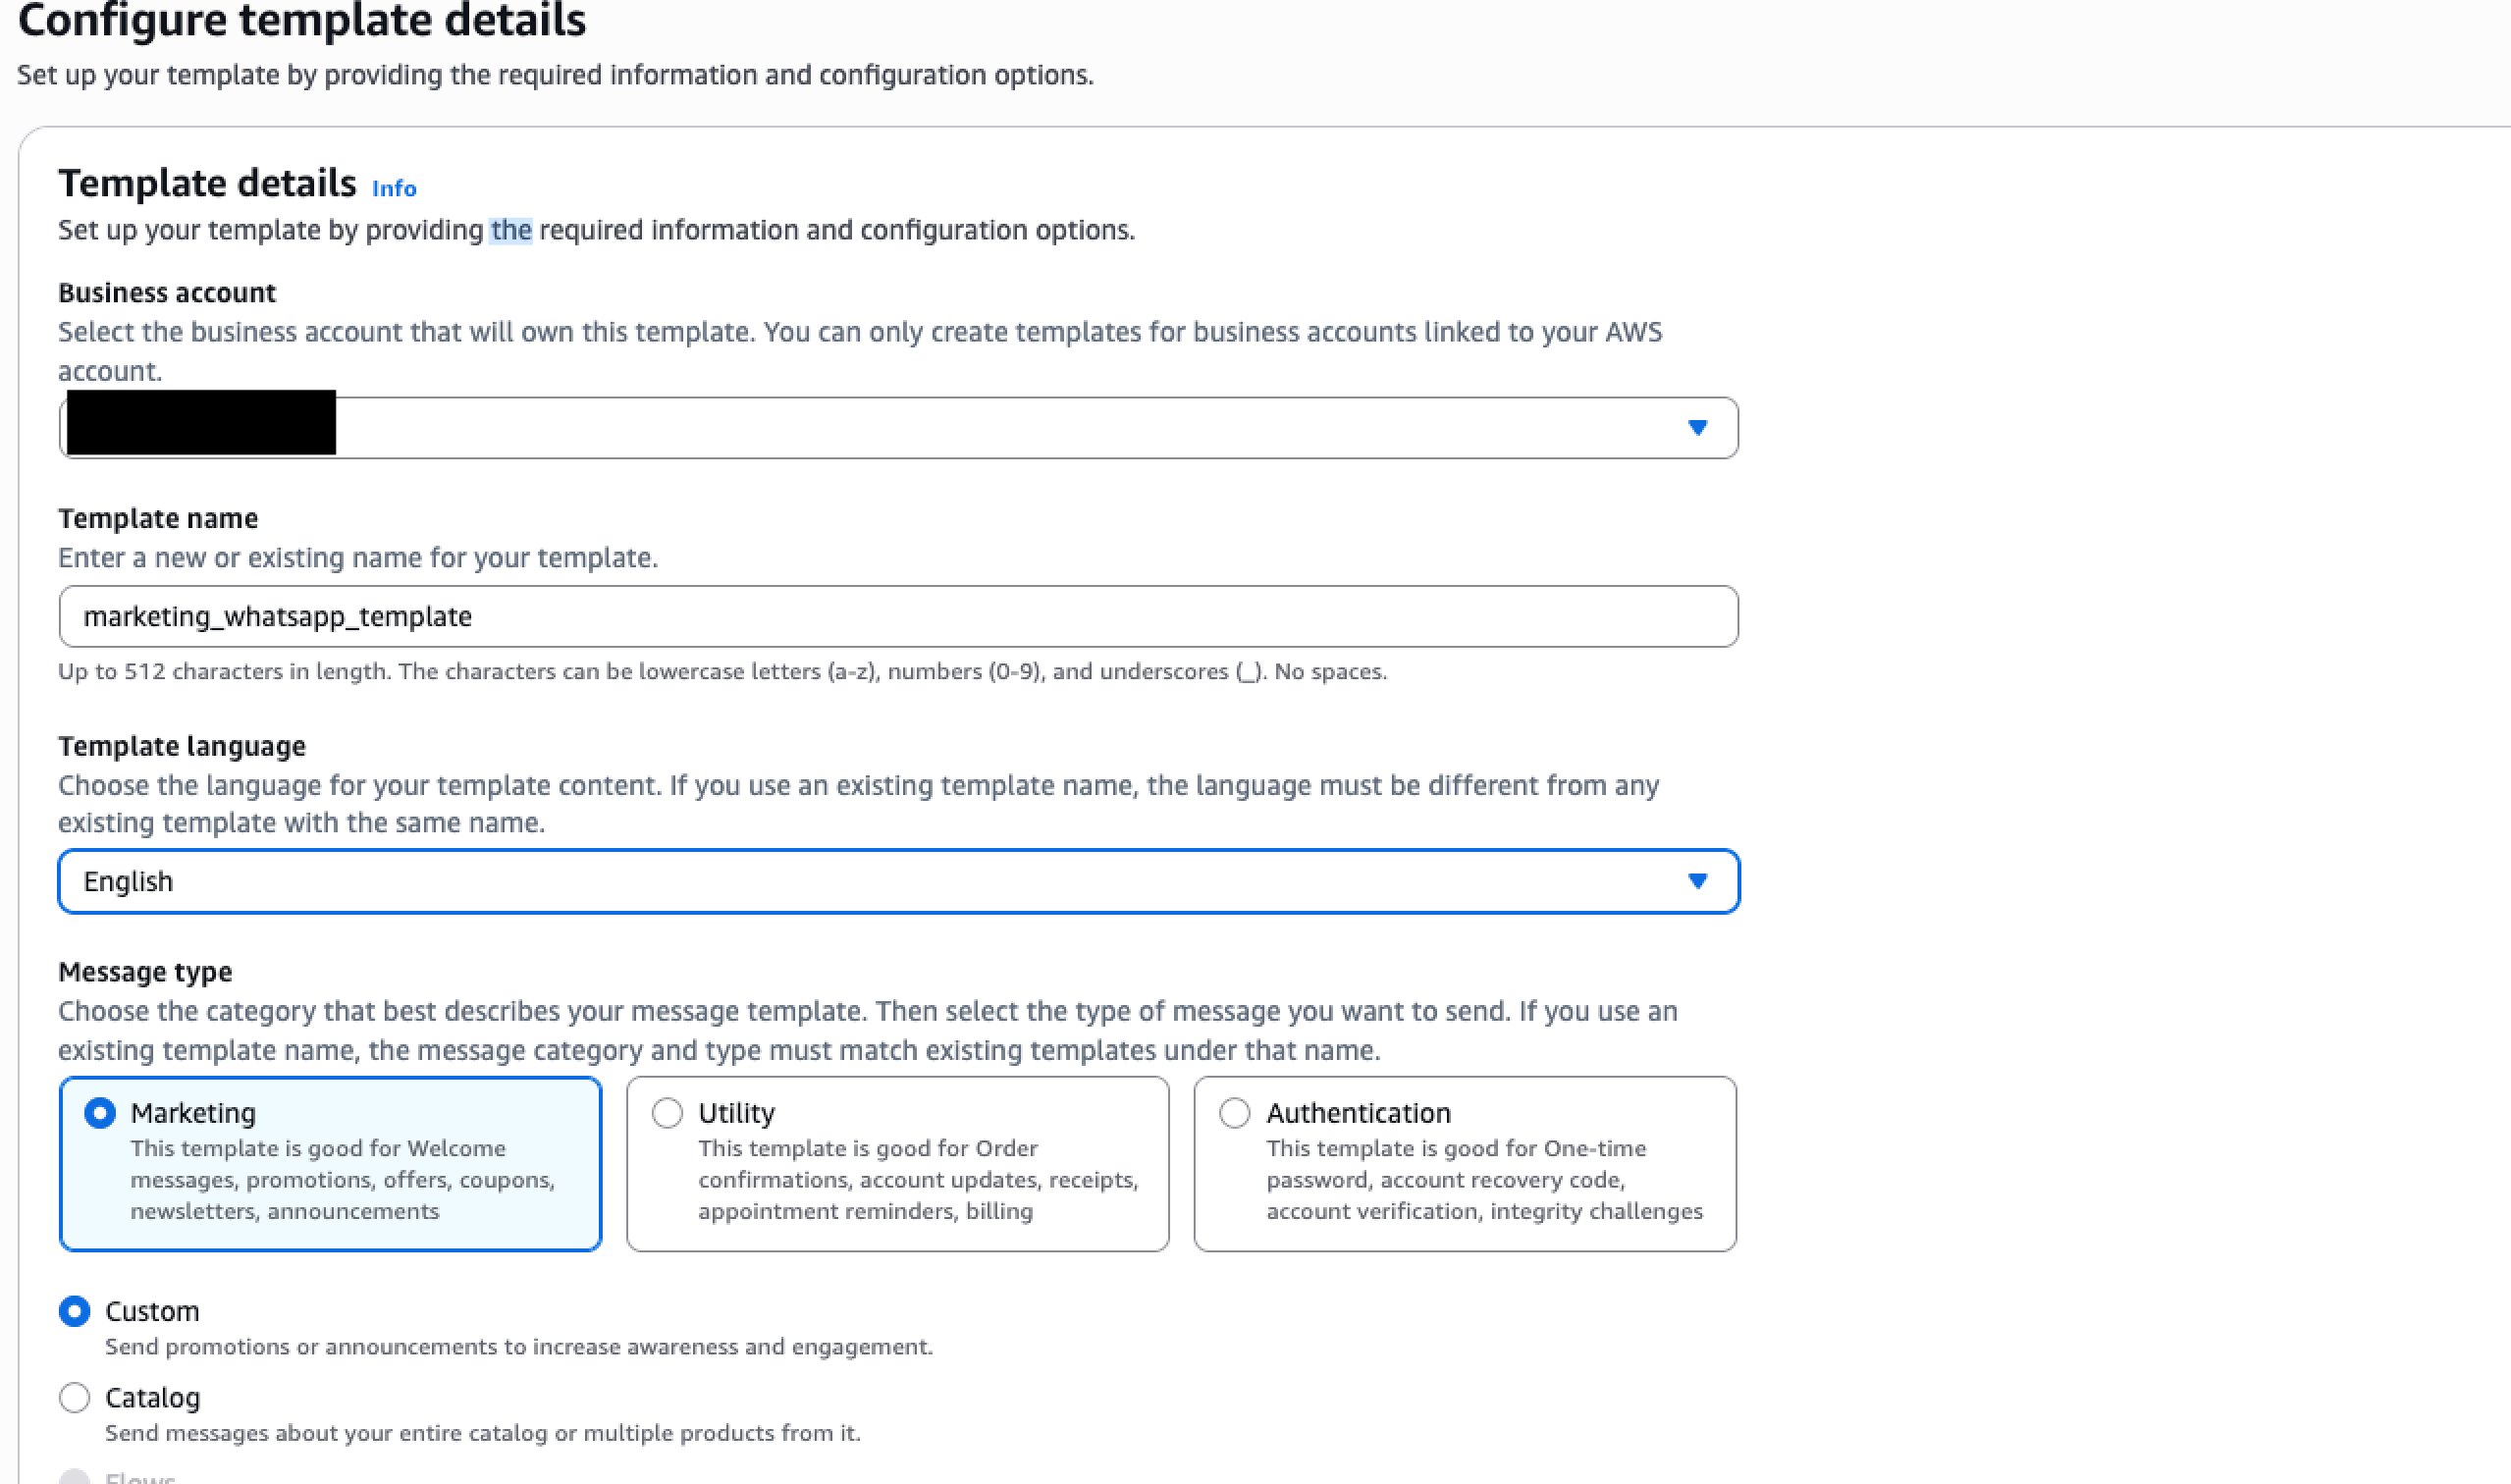
In the second screen, you can set the message content for the template including variables to dynamically populate when sending the message content.
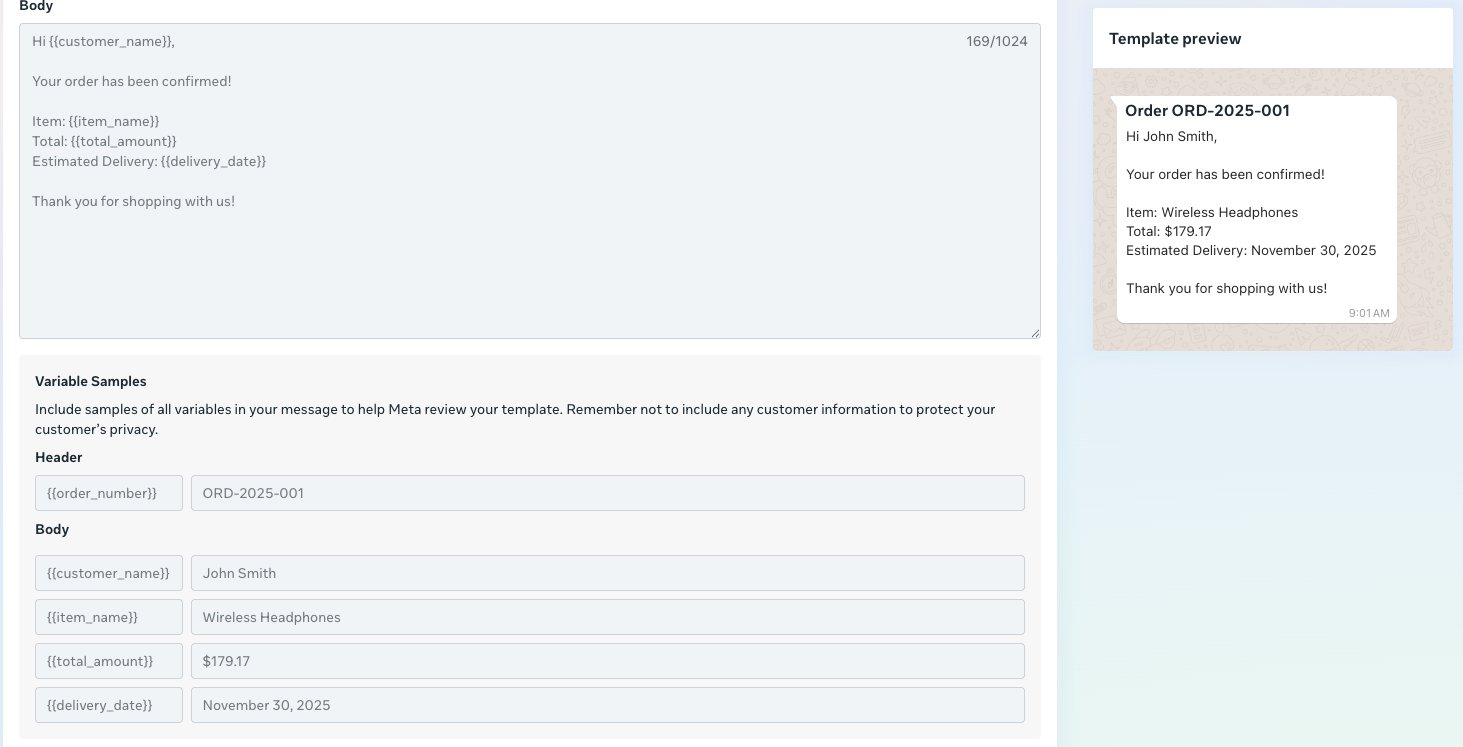
Approved message templates can be seen under the message template screen along with their approval status.
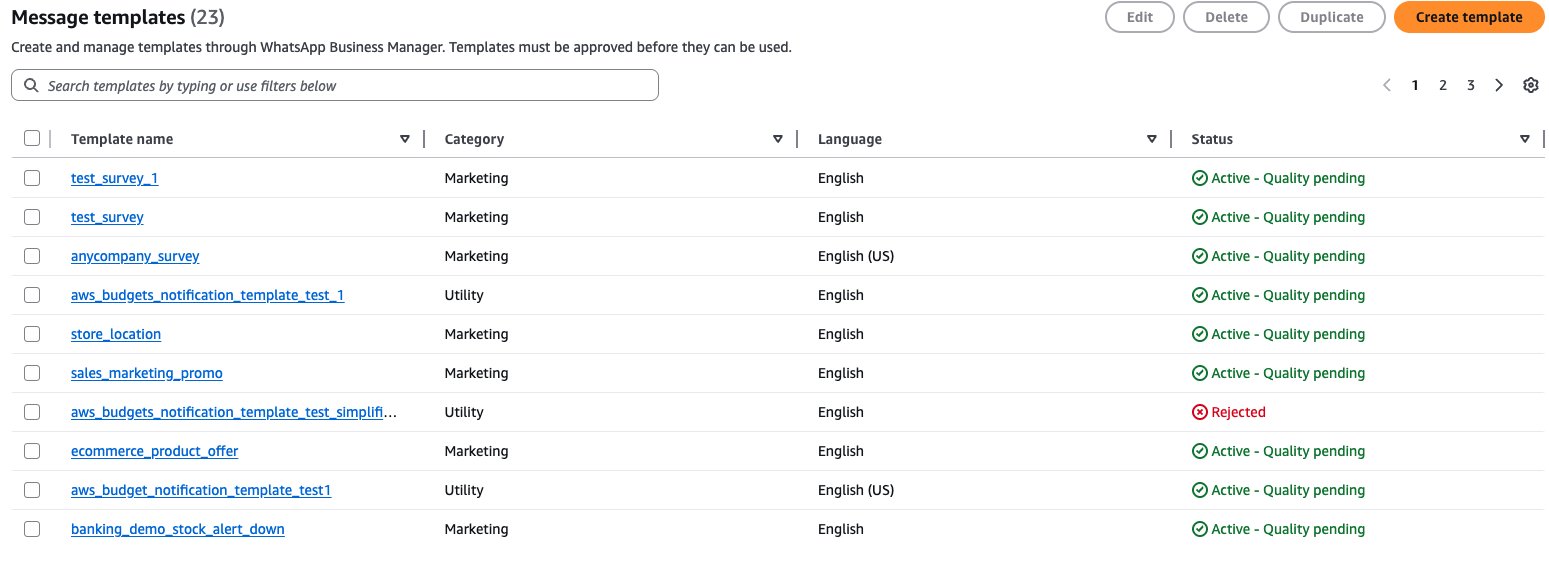
After your template is approved, you can send it with parameter values populated at send time.
Important: When sending the template message, you must use the same language and locale that you used when creating the template. For example, a language code of “en” isn’t the same as “en_US”.
Location messages share geographic coordinates with optional name and address information. For example, you can send a location for a store branch to a customer.
Step 1 — Create a file named store_location_template.json in your working directory with the following template definition:
Step 2 — Run the following CLI command to create the template. The –template-definition parameter references the JSON file that you previously created:
The following image is an example of a location message.
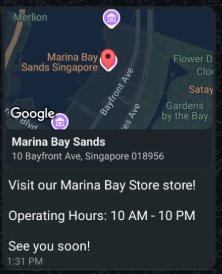
The following is a code example of the previous location message example.
Interactive messages provide pre-defined response options through buttons or lists. These messages must be sent within the 24-hour conversation window.
This example demonstrates collecting guest feedback using quick reply buttons for streamlined response collection.
Technical specifications:
The following image is an example of the Quick reply buttons message.
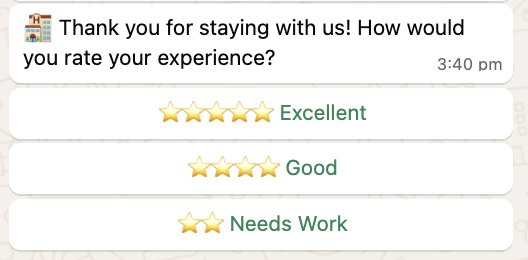
The following is a code example of the previous example image.
This example shows a restaurant menu using list messages for organized, scrollable content presentation.
Technical specifications:
The following is an image of a list message example.
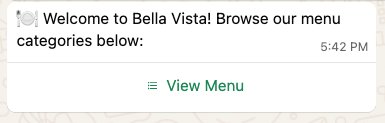
When the user expands the list, they can select individual items to add to their cart.
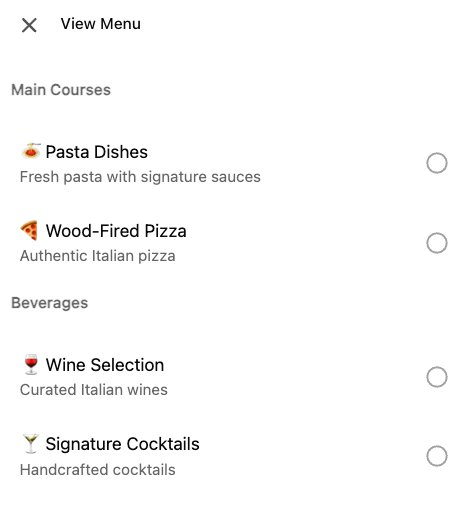
The following is the code example for the previously mentioned example.
Contact messages share vCard-formatted contact information, useful for sharing business contact details with customers.
The following is an image of an example contact message.
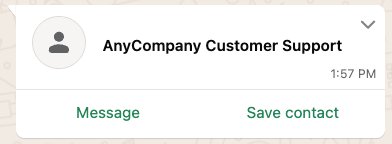
Customers can choose to directly message the contact, save the contact to their contacts list and view details about the contact in a pop up.
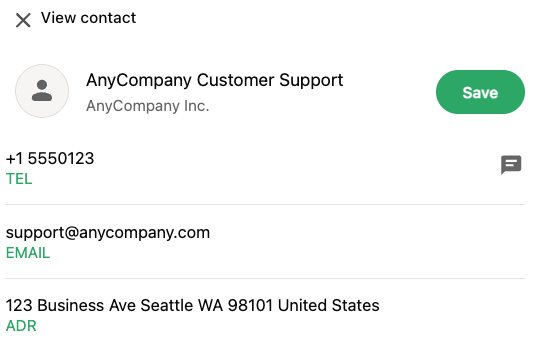
The following is a code example for the previously mentioned image example.
WhatsApp Flows can help power interactive experiences. Note that a verified WhatsApp Business Account is required to use WhatsApp Flows. There are two general types of WhatsApp Flows:
This is an example of a WhatsApp Flow without an endpoint that sends a product survey to customers. Since this flow doesn’t use an endpoint, the results can be viewed directly within WhatsApp Manager.
First create a WhatsApp Flow using the Flows Playground on the Meta for Developers website.
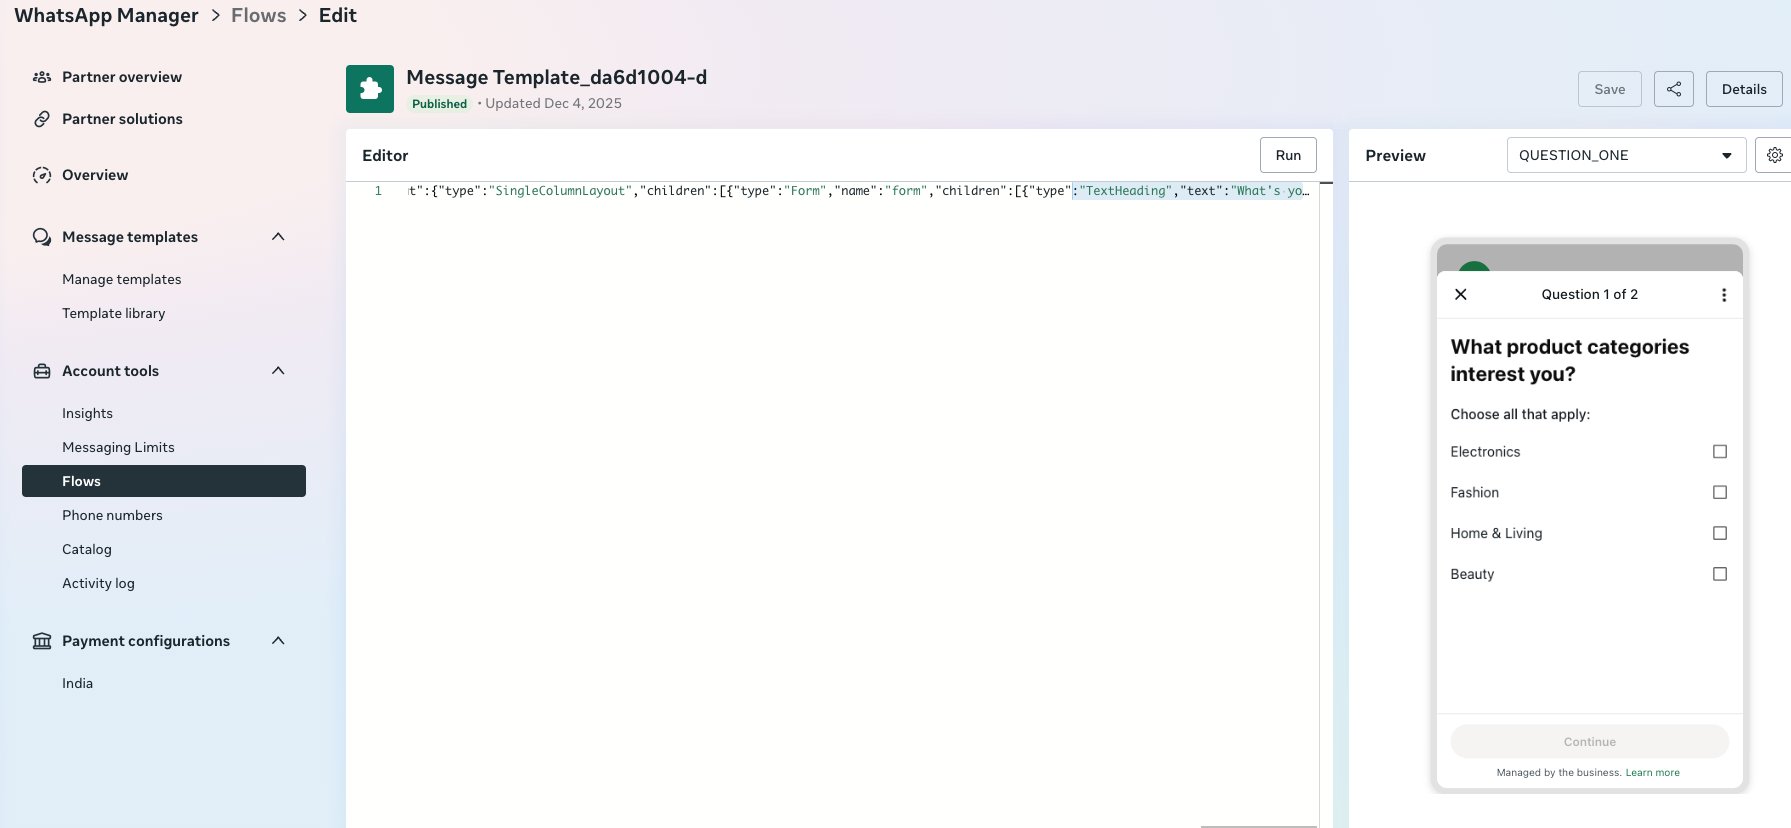
You can use the following JSON in the editor to use the example flow that we’re creating.
Afterwards you will be prompted to create the template to attach to the flow.
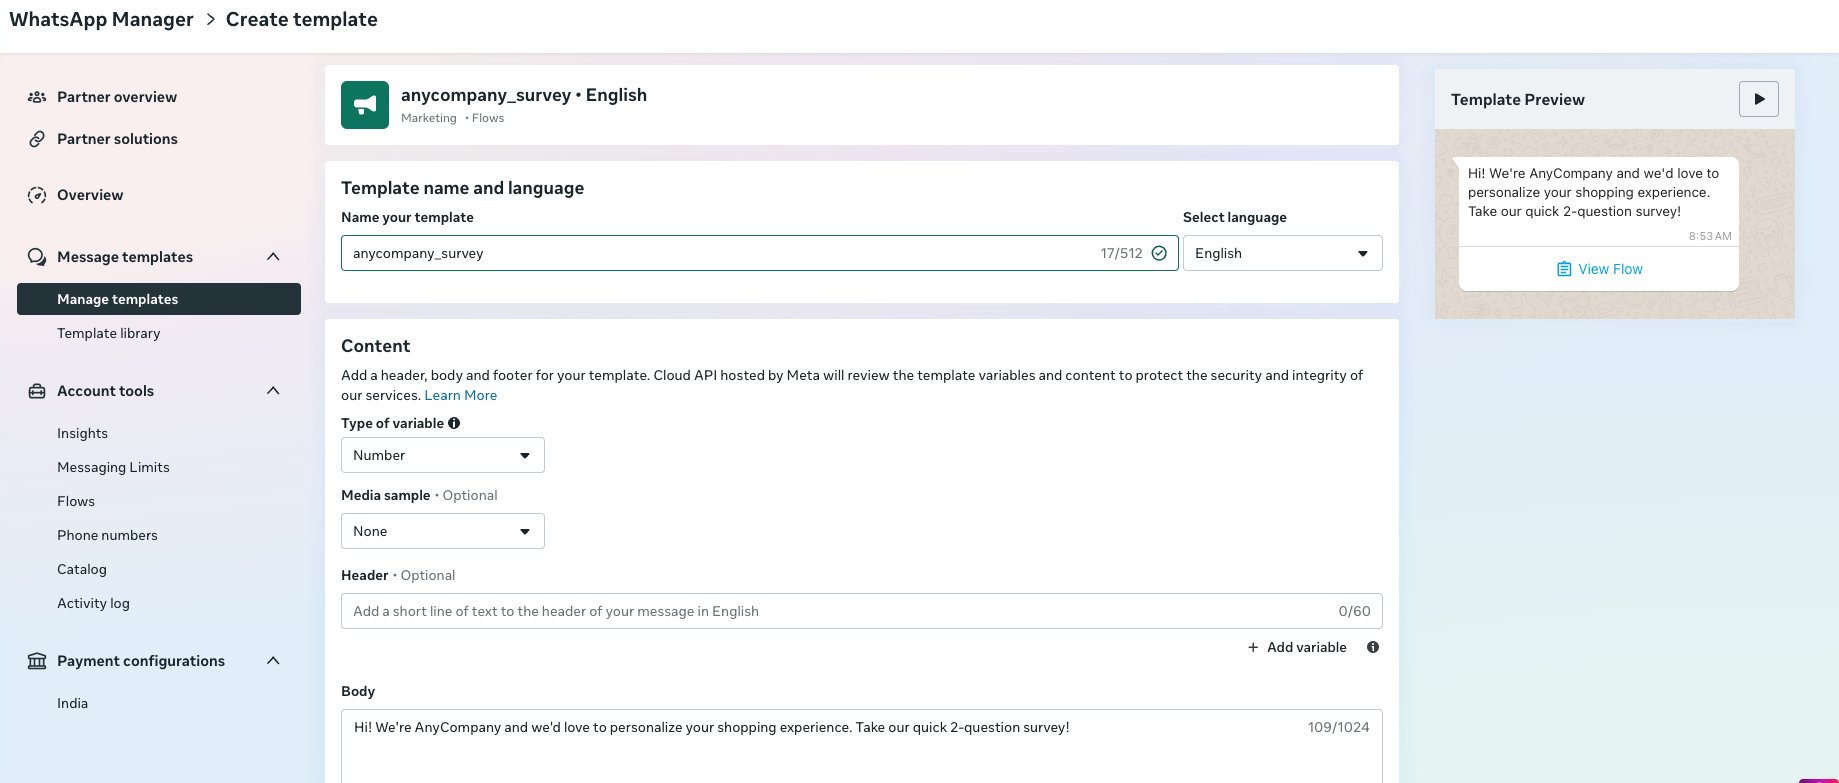
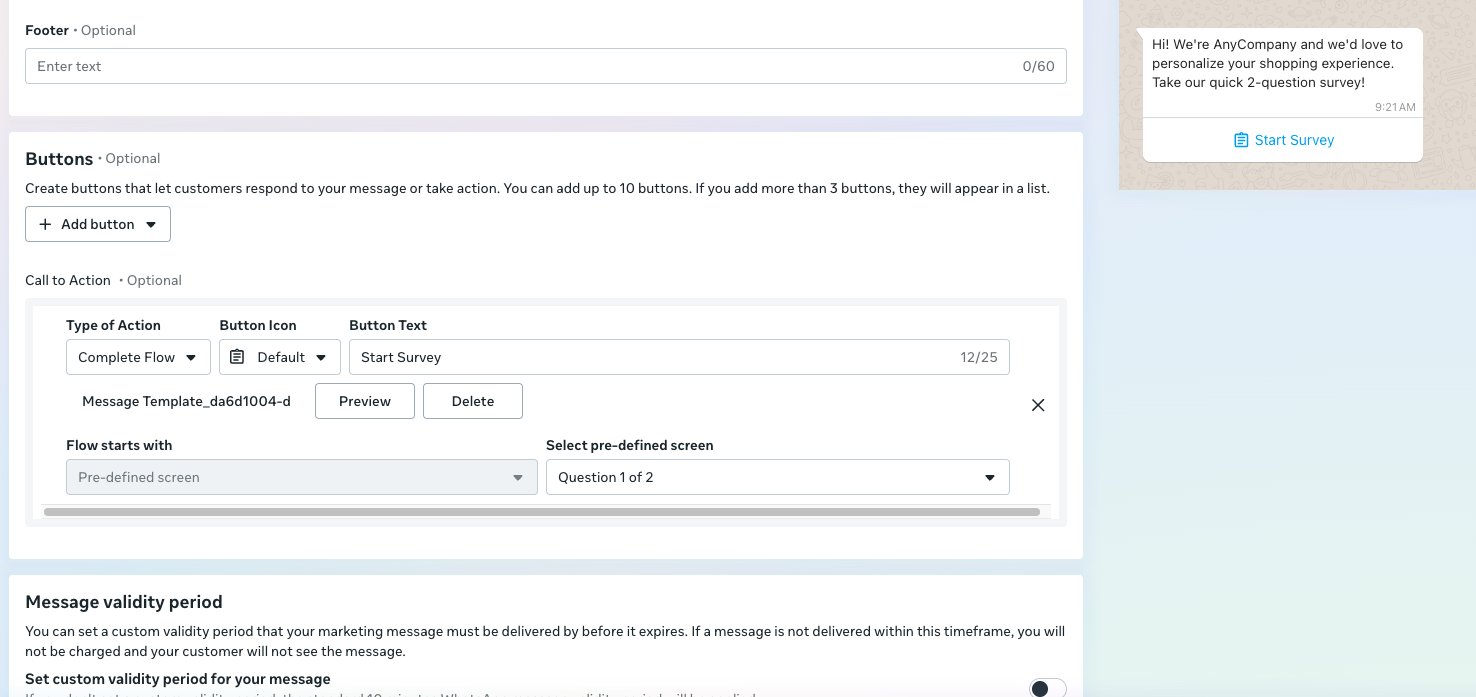
Step 1 — Create a file named anycompany_survey_template.json in your working directory with the following template definition. Notice that the Flow JSON is embedded directly in the flow_json field of the button component:
Step 2 — Run the following CLI command to create the template. The –template-definition parameter references the JSON file that you previously created:
After the Template and Flow are approved, a message can be sent with the following code.
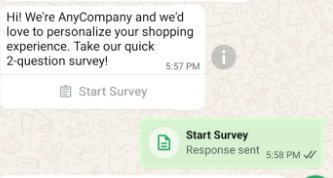
The Flow will appear with the message body specified and a link to start the survey.
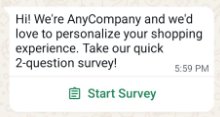
The recipient can provide their answers on each page of the Flow which can be submitted at the end.
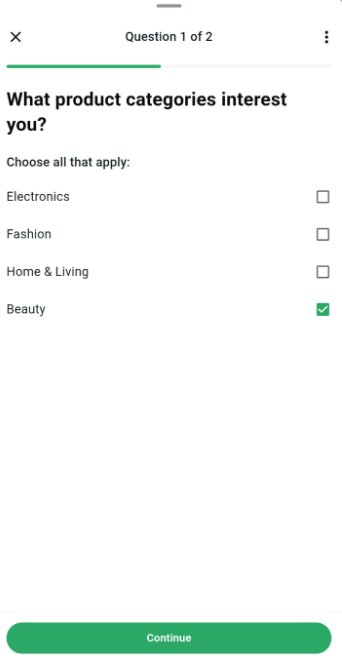
After providing inputs, the Flow will show a completed message.
To avoid incurring future charges, delete the resources that you created during this walkthrough:
For templates created in WhatsApp Manager, you can also delete them directly from the WhatsApp Business Manager interface on the Meta for Developers website.
In this post, you learned how to send various WhatsApp Business message types using AWS End User Messaging Social, including text messages, media messages, template messages, location messages, interactive messages, contact messages, and WhatsApp Flows.
AWS End User Messaging Social provides a managed API that removes the complexity of maintaining your own WhatsApp Business API integration, so you can focus on building engaging customer experiences. The service handles the heavy lifting of managing WhatsApp Business API connections, template approvals, and message delivery, while providing you with a unified, consistent API interface.
We’d love to hear about your experience! Share your use cases and implementation approaches in the comments.