On Thursday, April 3, 2025, Ivanti disclosed a critical severity vulnerability affecting Ivanti Connect Secure, Pulse Connect Secure, Policy Secure, and ZTA Gateways. CVE-2025-22457 is a stack-based buffer overflow vulnerability that allows remote, unauthenticated attackers to execute code on the target device. Ivanti’s advisory indicates that CVE-2025-22457 is known to be exploited in the wild; Google’s Mandiant division attributes this activity to suspected China-nexus actors.
Ivanti’s advisory indicates that the vulnerability was “initially identified as a product bug” and patched in Ivanti Connect Secure version 22.7R2.6 (released February 11, 2025). Per Mandiant, CVE-2025-22457 is “a buffer overflow with a limited character space, and therefore it was initially believed to be a low-risk denial-of-service vulnerability.” However, on April 3, Ivanti publicly acknowledged known exploitation in the wild of supported Ivanti Connect Secure and End-of-Support Pulse Connect Secure appliances for remote code execution in some customer environments.
Mitigation guidance
The following products and versions are vulnerable to CVE-2025-22457:
Ivanti Connect Secure 22.7R2.5 and prior
Pulse Connect Secure (End-of-Support) 9.1R18.9 and prior
Ivanti Policy Secure 22.7R1.3 and prior
ZTA Gateways 22.8R2 and prior
Ivanti has a full table of affected versions and corresponding solution estimates in their advisory.
A patch is available (initially released on February 11, 2025) for CVE-2025-22457 in Ivanti Connect Secure. However, the advisory states that patches for Ivanti Policy Secure and ZTA Gateways will not be available until April 21, 2025 and April 19, 2025, respectively. Pulse Connect Secure 9.1x reached End-of-Support on December 31, 2024 and won’t be patched. For the latest information, please refer to the Ivanti advisory.
Customers should apply the available Ivanti Connect Secure patch immediately, without waiting for a typical patch cycle to occur. Ivanti’s advisory notes that “Customers should monitor their external ICT and look for web server crashes. If your ICT result shows signs of compromise, you should perform a factory reset on the appliance and then put the appliance back into production using version 22.7R2.6.” Notably, ICT results may vary; a factory reset should be performed if exploitation is suspected, regardless of ICT results.
For the latest information, please refer to the vendor advisory.
Rapid7 customers
InsightVM and Nexpose customers will be able to assess their exposure to CVE-2025-22457 in Ivanti Connect Secure with a vulnerability check expected to be available in today’s (April 3, 2025) content release.
Rapid7 is warning customers of notable vulnerabilities in Next.js, a React framework for building web applications, and CrushFTP, a file transfer technology that has previously been targeted by adversaries.
CVE-2025-29927 is a critical improper authorization vulnerability in Next.js middleware that could (theoretically) allow an attacker to bypass authorization checks in a Next.js application, if the authorization check occurs in middleware.
No CVE has been assigned (as of March 25, 2025) to an unauthenticated HTTP(S) port access vulnerability in CrushFTP file transfer software
Neither of the above vulnerabilities is known to have been exploited in the wild as of Tuesday, March 25, 2025. CrushFTP has previously been exploited in the wild for adversary access to (and exfiltration of) sensitive data.
CrushFTP unauthenticated HTTP(S) port access vulnerability (no CVE)
On Friday, March 21, 2025, file transfer software maker CrushFTP disclosed a new vulnerability to customers via email:
Note: While the email image above indicates only CrushFTP v11 is affected by the still-CVE-less (as of March 25) unauthenticated port access vulnerability, the extremely sparse vendor advisory indicates that both CrushFTP v10 and v11 are affected. According to the vendor, the issue is not exploitable if customers have the DMZ function of CrushFTP in place.
Mitigation guidance: File transfer technologies are high-value targets for ransomware and other adversaries looking to quickly gain access to and exfiltrate sensitive data.Per the email sent to CrushFTP customers on Friday, March 21, the vulnerability is fixed in CrushFTP v11.3.1 (and later). Customers should update immediately, without waiting for a regular patch cycle to occur.
Next.js CVE-2025-29927
CVE-2025-29927 stems from logic associated with how middleware is handled by the application — specifically, an attacker can provide a header in any request to bypass application middleware. Application middleware can perform any number of tasks, and it can stack so that multiple layers of middleware can be configured, with each able to modify the request/response passed to it. Common use cases of middleware include authentication/authorization, CSP validation, URL rewriting/redirection etc.
As the vulnerability affects an application framework, and the application middleware configuration can vary greatly, so too does the potential impact of exploiting the vulnerability. Based on Rapid7’s analysis, there is no ‘one-size-fits-all’ determination of risk/impact for CVE-2025-29927 (which is a common scenario for framework and library vulns). The most severe potential impact likely comes in the form of authentication bypass, but would still be highly application-dependent — the impact of bypassing authentication for a hobbyist “To do list” application is very different from theoretically bypassing authentication in an enterprise application utilising Next.js.
Organizations should consider whether their applications are relying solely on the middleware for authentication. It may be that the application uses middleware, but is just acting as a front end to back-end APIs that are dealing with server-side authentication logic. Bypassing the front-end Next.js middleware would not affect the back end’s ability to authenticate users.
As an example of how a more measured view can change the outlook, a Red Hat advisory for CVE-2025-29927 originally listed two products as affected: Red Hat Trusted Artifact Signer and Streams for Apache Kafka 2. Now these have been removed and classified as “Not affected,” presumably following further review. The advisory was updated with the following: “Red Hat Trusted Artifact Signer and Streams for Apache Kafka 2 are not affected by this vulnerability as they do not use Next.js for any authorization functionality.”
Mitigation guidance: Per the Next.js advisory, CVE-2025-29927 affects the following versions of Next.js:
>= 13.0.0, < 13.5.9 (fixed in 13.5.9)
>= 14.0.0, < 14.2.25 (fixed in 14.2.25)
>= 15.0.0, < 15.2.3 (fixed in 15.2.3)
>= 11.1.4, < 12.3.5 (fixed in 12.3.5)
Rapid7 customers
InsightVM and Nexpose customers who run CrushFTP on Linux can assess their exposure to the no-CVE unauthenticated HTTP(S) port access issue with a vulnerability check available in the Friday, March 21 content release.
Our InsightVM coverage team is assessing the feasibility of adding a vulnerability check for Next.js CVE-2025-29927. We will update this blog with further information no later than 6 AM ET on Wednesday, March 26, 2025.
On Wednesday, March 19, 2025, backup and recovery software provider Veeam published a security advisory for a critical remote code execution vulnerability tracked as CVE-2025-23120. The vulnerability affects Backup & Replication systems that are domain joined. Veeam explicitly mentions that domain-joined backup servers are against security and compliance best practices, but in reality, we believe this is likely to be a relatively common configuration.
Veeam’s advisory indicates that the vulnerability is authenticated, though the CVSS score for CVE-2025-23120 is listed as 9.9. The advisory itself states that “authenticated domain users” can exploit the vulnerability but says little else — it’s possible that additional exploitation criteria will be published later on. According to Veeam, all supported versions of Backup & Replication are affected.
No public proof-of-concept exploit has been released (at time of this blog’s publication). Veeam Backup & Replication has a very large deployment footprint, and backup solutions are commonly targeted by threat actors. Veeam Backup & Replication should not be exposed to the internet and makes for a more effective internal attack vector than an external vector. Still, plenty of previous Veeam Backup & Replication vulnerabilities have been exploited in the wild, including by ransomware groups.
As we have mentioned previously, more than 20% of Rapid7 incident response cases in 2024 involved Veeam being accessed or exploited in some manner, typically once an adversary has already established a foothold in the target environment.
Mitigation guidance
Veeam Backup & Replication 12.3.0.310 and all earlier version 12 builds are vulnerable to CVE-2025-23120, per the vendor advisory.
Customers should update to the latest version of the software (12.3 build 12.3.1.1139) immediately, without waiting for a regular patch cycle to occur. Per the vendor, unsupported software versions were not tested but should be considered vulnerable.
Rapid7 customers
InsightVM and Nexpose customers will be able to assess their exposure to CVE-2025-23120 with a vulnerability check expected to be available in tomorrow’s (Thursday, March 20) content release.
Here at Rapid7, our usual bar for calling a vulnerability an emergent threat is either known exploitation at scale, or likelihood of exploitation at scale. Apache Tomcat CVE-2025-24813 fulfills neither of these criteria, despite a variety of news headlines alleging broad exploitation in the wild. Tomcat is widely deployed and has seen a number of severe vulnerabilities over the years that have had specific configuration dependencies for successful exploitation — this one follows the same pattern.
TL;DR: Patch, but there’s no need to panic. Here’s what you need to know:
CVE-2025-24813 is an unauthenticated remote code execution vulnerability in Apache Tomcat’s partial PUT feature disclosed on March 10, 2025. Fixed versions are available.
Under specific circumstances, successful exploitation allows attackers to execute code remotely on target systems via unsafe deserialization.
Vulnerability details and proof-of-concept (PoC) exploit code are both publicly available.
Based on our analysis and those of other research firms, the conditions required for successful exploitation appear to be specific, non-default, and uncommon.
CVE-2025-24813 has reportedly been exploited in the wild; however, Rapid7 has been unable to confirm any successful exploitation occurring against real-world production environments. We assess that “exploitation” in this context likely means unsuccessful exploit attempts rather than successful compromise of production systems.
Broad exploitation is unlikely given the specific vulnerable configuration requirements (see Exploitability requirements below).
Rapid7 researchers have tested publicly available PoC code and investigated the conditions Apache indicated were required for exploitation. Like other researchers, our team found that the vendor’s exploitable configuration information differs from what we observed during testing. Additionally, our team assessed the exploitable configuration to be relatively uncommon. Based on a GitHub code search query, only a small number of open-source Tomcat projects published publicly on GitHub are using write-enabled default servlet configurations (a pre-requisite for exploitation) — approximately 200, and most have fewer than 30 stars. Rapid7’s vulnerability research team has a full testing report here.
Exploitability requirements
Per the advisory, an attacker could view security sensitive files and/or inject content into those files if ALL of the following were true:
writes enabled for the default servlet (disabled by default)
support for partial PUT (enabled by default)
a target URL for security sensitive uploads that was a sub-directory of a target URL for public uploads (ed: Rapid7 and other researchers found this to be unnecessary for exploitation)
attacker knowledge of the names of security sensitive files being uploaded (ed: Rapid7 and other researchers found this to be unnecessary for exploitation)
the security sensitive files also being uploaded via partial PUT (ed: Rapid7 and other researchers found this to be unnecessary for exploitation)
An attacker could achieve remote code execution if ALL of the following were true:
writes enabled for the default servlet (disabled by default)
support for partial PUT (enabled by default)
application was using Tomcat’s file-based session persistence (ed: disabled by default) with the default storage location
application included a library that may be leveraged in a deserialization attack (ed: this is the case for many Java applications)
Mitigation guidance
The following versions of Apache Tomcat are affected:
Apache Tomcat 11.0.0-M1 to 11.0.2 (fixed in 11.0.3 or later)
Apache Tomcat 10.1.0-M1 to 10.1.34 (fixed in 10.1.35 or later)
Apache Tomcat 9.0.0.M1 to 9.0.98 (fixed in 9.0.99 or later)
For the latest information, please see the Apache Software Foundation’s advisory.
Rapid7 customers
InsightVM and Nexpose customers can assess their exposure to CVE-2025-24813 with pre-existing vulnerability checks.
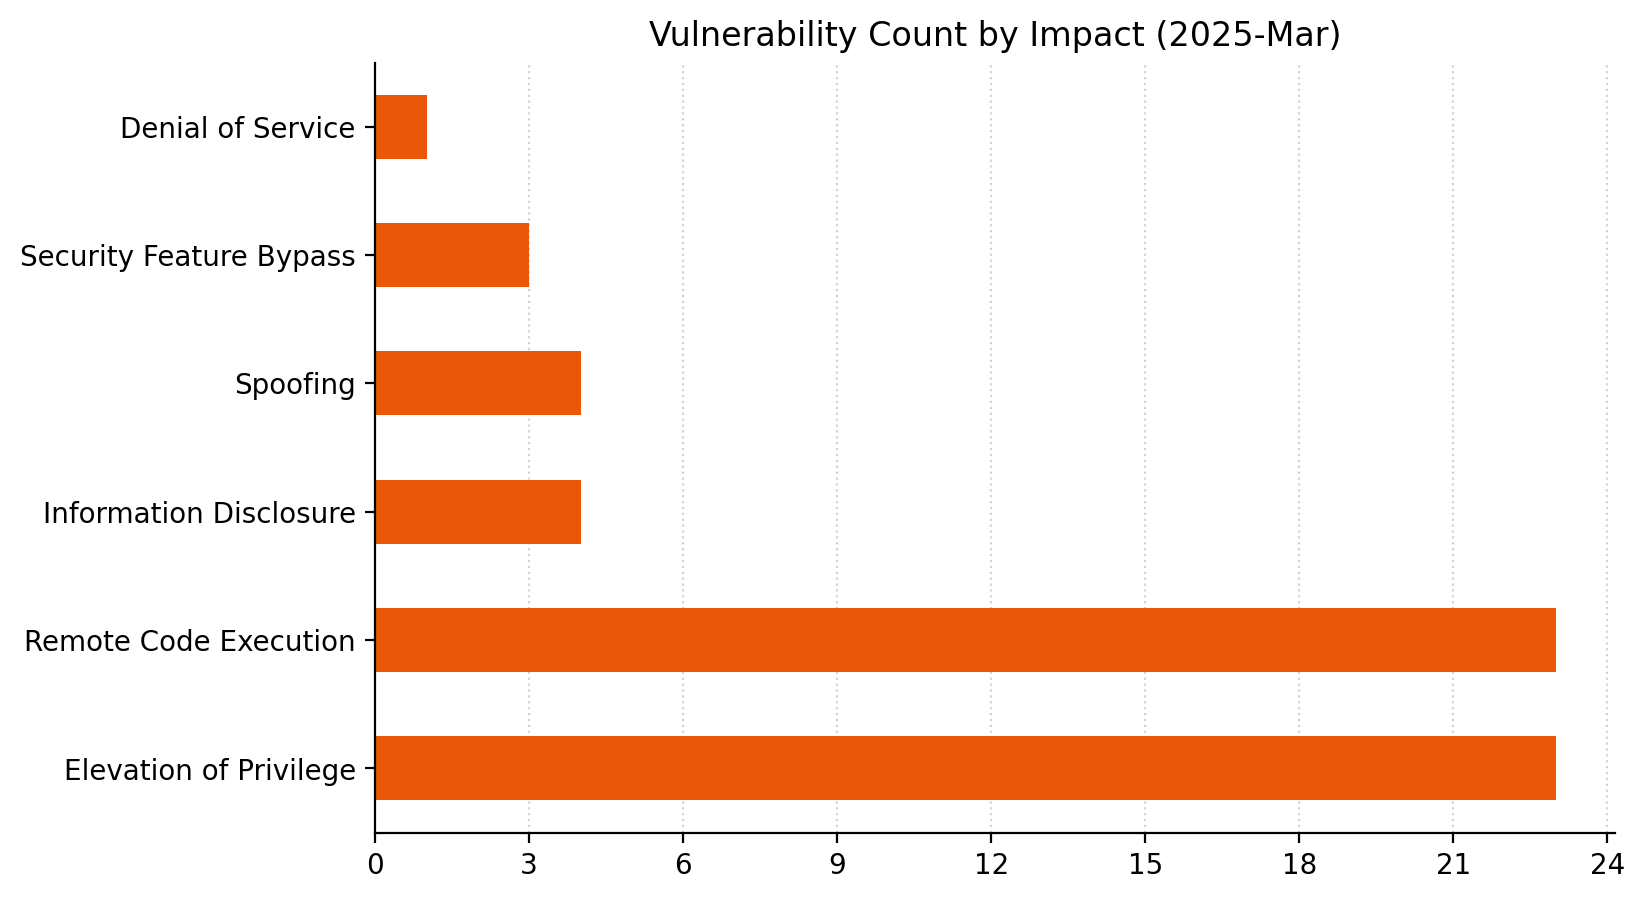
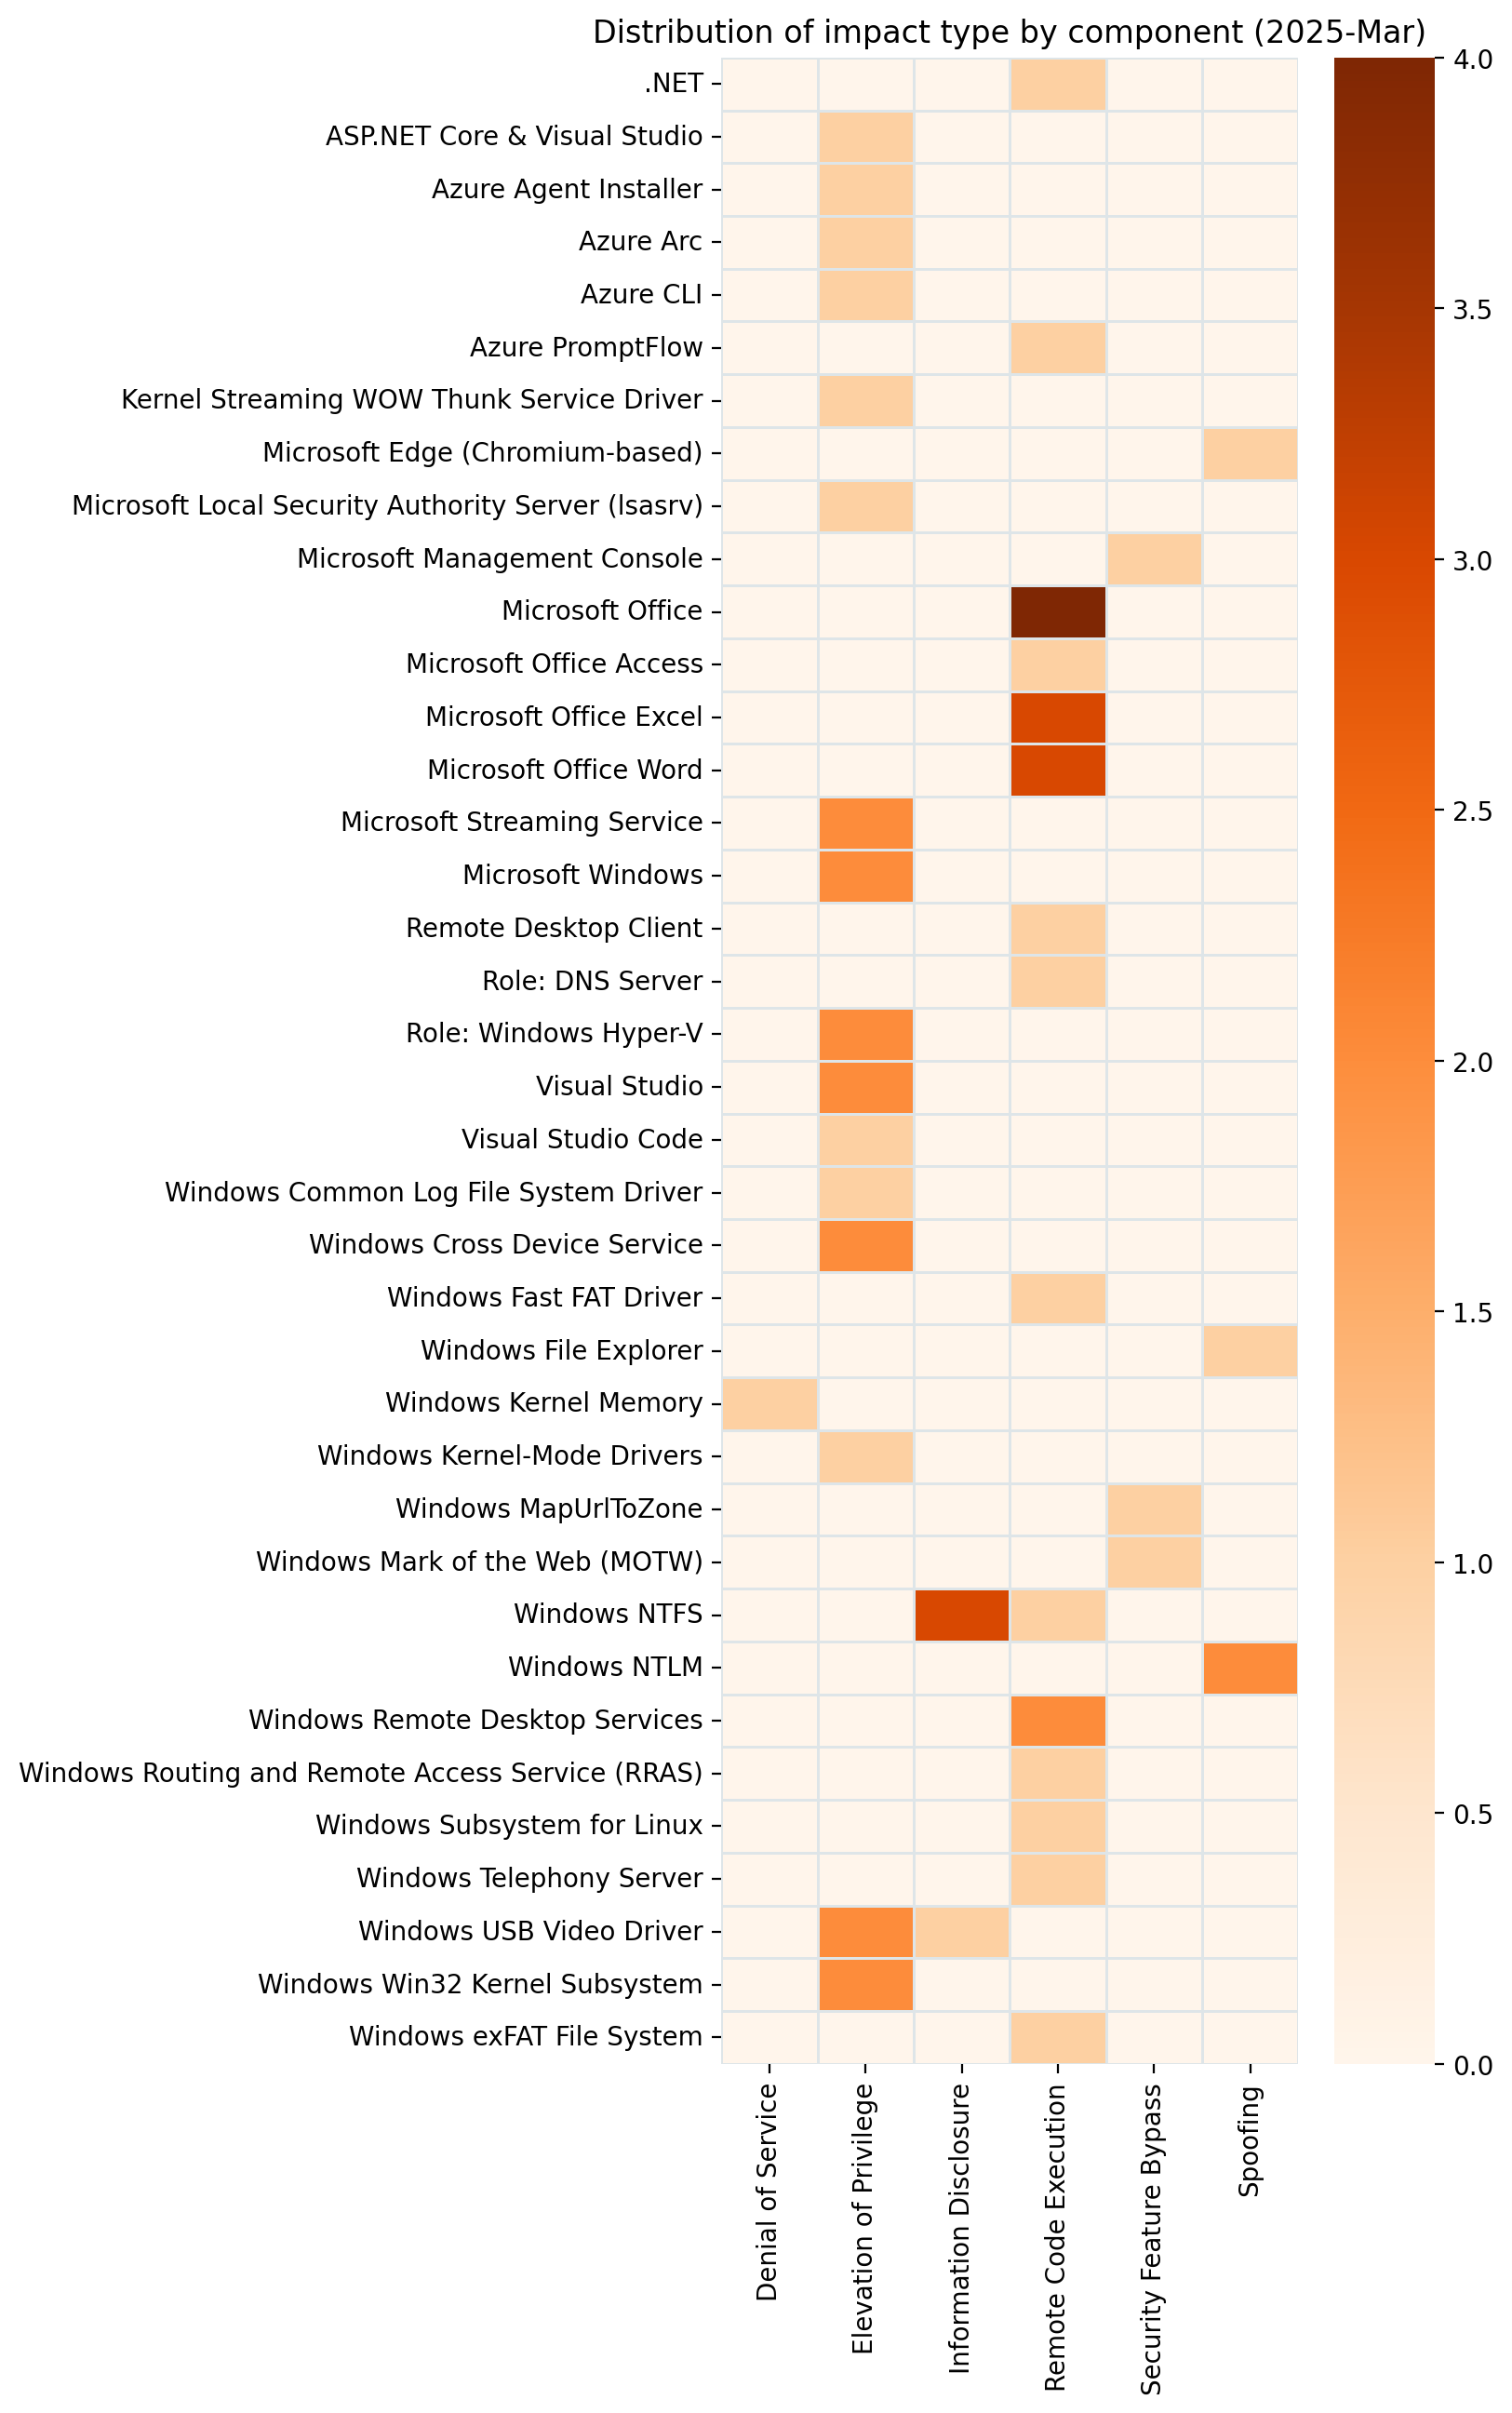
Microsoft is addressing 57 vulnerabilities this March 2025 Patch Tuesday, which is a similar volume to last month. However, Microsoft has evidence of in-the-wild exploitation for as many as six of the vulnerabilities published today, and CISA KEV already lists all of them. Microsoft is also aware of public disclosure for one other vulnerability. This is now the sixth consecutive month where Microsoft has published zero-day vulnerabilities on Patch Tuesday without evaluating any of them as critical severity at time of publication. Today also sees the publication of six critical remote code execution (RCE) vulnerabilities. Ten browser vulnerabilities have already been published separately this month, and are not included in the total.
Win32 kernel subsystem: zero-day EoP
Older Windows products receive a patch today for CVE-2025-24983, which is an elevation of privilege vulnerability in the Win32 kernel subsystem. Microsoft is aware of exploitation in the wild. Since no user interaction is required, and successful exploitation leads to SYSTEM privileges, this isn’t one to ignore, even if the attacker must win a race condition, which does raise the bar for entry somewhat. Microsoft Windows 11 and Server 2019 onwards are not listed as receiving patches, so are presumably not vulnerable. It’s not clear why newer Windows products dodged this particular bullet; the Windows 32 subsystem is still presumably alive and well, since there is no apparent mention of its demise on the Windows client OS deprecated features list.
NTFS USB attack: zero-day information disclosure
Defense-in-depth practitioners have been limiting and monitoring access to USB ports for years now, and today brings further evidence for the value of locking things down, in the form of CVE-2025-24984, an information disclosure vulnerability in NTFS. Microsoft has evidence of exploitation in the wild, and functional exploit code. This vulnerability has a thus-far-unique combination of attributes: the attack vector is physical — the advisory describes a malicious USB drive as the delivery mechanism — and the weakness is CWE-532: Insertion of Sensitive Information into Log File. The advisory doesn’t quite join the dots, but successful exploitation appears to mean that portions of heap memory could be improperly dumped into a log file, which could then be combed through by an attacker hungry for privileged information. A relatively low CVSSv3 base score of 4.6 reflects the practical difficulties of real-world exploitation, but a motivated attacker can sometimes achieve extraordinary results starting from the smallest of toeholds, and Microsoft does rate this vulnerability as important on its own proprietary severity ranking scale.
NTFS VHD attack: zero-day information disclosure
If you like NTFS zero-day vulnerabilities, then today’s your lucky day! CVE-2025-24991 describes an out-of-bounds read in NTFS leading to information disclosure, specifically disclosure of small portions of heap memory. An attacker would need to trick a user into mounting a malicious VHD (Virtual Hard Disk), and that alone would be enough to trigger the vulnerability. The advisory does not explain how the attacker would exfiltrate the data, but clearly it’s practically possible, since Microsoft claims evidence of exploitation in the wild.
NTFS VHD attack: zero-day code execution
If you like NTFS zero-day vulnerabilities, but find information disclosure a bit pedestrian, then CVE-2025-24993 might be just what you’re after: exploitation requires that the user mount a malicious VHD, which then leads to heap-based buffer overflow, and the potential for local code execution. As is standard for a certain type of code execution vulnerability, the advisory somewhat awkwardly clarifies that the word “remote” in the title refers to the location of the attacker, and that the attack itself is carried out locally. The advisory doesn’t specify the context of code execution, but it’s a safe assumption that the end goal here is SYSTEM, since the attacker or a user must already execute code in the context of the user to trigger the vulnerability. The CVSSv3 base score of 7.8 reflects the potentially valuable reward for exploitation and low attack complexity, but is held back by the requirement for user interaction.
Fast FAT VHD attack: zero-day code execution
The Windows Fast FAT file system driver is the site of CVE-2025-24985, which Microsoft describes as a code execution vulnerability. Exploitation requires that the user mount a malicious VHD, leading to integer overflow or wraparound. Microsoft claims to have confirmed evidence of exploitation in the wild. The acknowledgments sections for CVE-2025-24984, CVE-2025-24991, CVE-2025-24993, and CVE-2025-24985 all credit an anonymous reporter. More than likely this is the same entity in each case, given the similarities between the four vulnerabilities.
Microsoft Management Console: zero-day security feature bypass
It’s been a few months since we saw a zero-day vulnerability in the Microsoft Management Console, but today brings us CVE-2025-26633, a security feature bypass for which Microsoft is aware of exploitation in the wild, as well as functional exploit code floating around somewhere out there on the internet. Successful exploitation leads to an outcome which isn’t specified by the advisory, but since the Microsoft Management Console has a feature set which includes the creation, hosting, and distribution of custom tools for the administrative management of both hardware and software for any supported version of Windows, it’s easy enough to see why an attacker might be interested. The advisory does mention that both preparation of the target environment and subsequent user interaction are required for successful exploitation, which would require the user to open a malicious file.
Microsoft Access: zero-day code execution
CVE-2025-26630 describes a remote-but-actually-local code execution vulnerability in Microsoft Access. Exploitation requires that the user open a malicious file. Microsoft is aware of public disclosure, but considers exploitation less likely. The weakness is our old friend CWE-416: Use After Free. Beyond that, the advisory is short on detail, but does claim that the Preview Pane is not an attack vector, so that’s a silver lining for this particular cloud. Going by the acknowledgements section of the advisory, it seems likely that relative newcomer Unpatched.ai intends to continue to shake things up, since they were also credited with a trio of zero-day Access vulnerabilities published back in January.
WSL magic email attack: critical RCE
The Windows Subsystem for Linux (WSL2) kernel receives a patch today for an arbitrary code execution vulnerability. Microsoft doesn’t claim evidence of public disclosure or in-the-wild exploitation for CVE-2025-24084, but does rank it as critical using its own proprietary severity ranking scale, which goes beyond what the already-significant CVSSv3 base score of 8.4 would suggest. The advisory describes multiple possible attack vectors, but in the worst case, there is no requirement for user interaction, since simply receiving a malicious email would be enough to trigger the vulnerability. The advisory does not clarify the context of code execution, but the magic email attack vector is alarming. Patch accordingly.
Malicious RDP server: critical RCE
How much do you trust the RDP server you’re about to connect to? An attacker in control of a malicious RDP server simply has to wait for a client vulnerable to CVE-2025-26645 to connect in order to achieve remote code execution on the client. Microsoft has assigned a CVSSv3 base score of 8.8 and a severity ranking of critical. While none of us should be connecting to RDP servers we’re not familiar with, an attacker might well see CVE-2025-26645 as a great opportunity for lateral movement and footprint expansion through the network.
Microsoft lifecycle update
In Microsoft product lifecycle news, SQL Server 2019 moved from mainstream support to extended support on 2025-02-28. Looking ahead, Visual Studio App Center will be retired on 2025-03-31, and Dynamics GP 2015 moves past the end of extended support on 2025-04-08.
On Tuesday, March 4, 2025, Broadcom published a critical security advisory (VMSA-2025-0004) on 3 new zero-day vulnerabilities affecting multiple VMware products, including ESXi, Workstation, and Fusion. The most severe of the vulnerabilities is CVE-2025-22224, a critical vulnerability in ESXi and Workstation. Notably, these are not remotely exploitable vulnerabilities — they require an attacker to have existing privileged access on a VM that is running on an affected VMware hypervisor.
CVE-2025-22224 (CVSS 9.3): A Time-of-Check Time-of-Use (TOCTOU) vulnerability in VMware ESXi and Workstation that can lead to an out-of-bounds write condition. An attacker with local administrative privileges on a virtual machine could exploit this issue to execute code as the virtual machine’s VMX process running on the host.
CVE-2025-22225 (CVSS 8.2): An arbitrary write vulnerability in VMware ESXi that allows an attacker with privileges within the VMX process to trigger an arbitrary kernel write leading to an escape of the sandbox.
CVE-2025-22226 (CVSS 7.1): An information disclosure vulnerability in VMware ESXi, Workstation, and Fusion that arises from an out-of-bounds read in the Host Guest File System (HGFS). An attacker with administrative privileges to a virtual machine could exploit this issue to leak memory from the VMX process.
Broadcom has published an FAQ with additional information for VMware customers.
All 3 vulnerabilities were reported to Broadcom by Microsoft Threat Intelligence Center. Broadcom’s advisory indicates for all 3 CVEs that Broadcom “has information to suggest that exploitation has occurred in the wild.” Shortly after Broadcom published their advisory, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added all 3 CVEs to the Known Exploited Vulnerabilities (KEV) list.
Based on the information in the advisory, it appears that the 3 vulnerabilities can be chained together: “This is a situation where an attacker who has already compromised a virtual machine’s guest OS and gained privileged access (administrator or root) could move into the hypervisor itself.”
There is no known publicexploit code for any of the CVEs at time of publication. Nevertheless, given that ESXi hypervisors are popular targets for both financially motivated and state-sponsored adversaries, Rapid7 recommends applying vendor-supplied fixes on an expedited basis.
Affected products
The following products are vulnerable to CVE-2025-2224, CVE-2025-22225, and CVE-2025-2226:
Broadcom VMware ESXi 7.0 and 8.0
Broadcom VMware Cloud Foundation 4.5.x and 5.x
Broadcom VMware Telco Cloud Platform 5.x, 4.x, 3.x, and 2.x
Broadcom VMware Telco Cloud Infrastructure 3.x and 2.x
The following products are vulnerable to CVE-2025-22224 and CVE-2025-22226:
Broadcom VMware Workstation 17.x
The following product is vulnerable to CVE-2025-22226:
Broadcom VMware Fusion 13.x
For the most complete information on affected and fixed versions, see Broadcom’s advisory and FAQ.
Rapid7 customers
InsightVM and Nexpose customers will be able to assess their exposure to CVE-2025-22224, CVE-2025-22225, and CVE-2025-22226 on Broadcom VMware ESXi hypervisors, Fusion, and Workstation products with vulnerability checks expected to be available in today’s (Tuesday, March 4) content release.
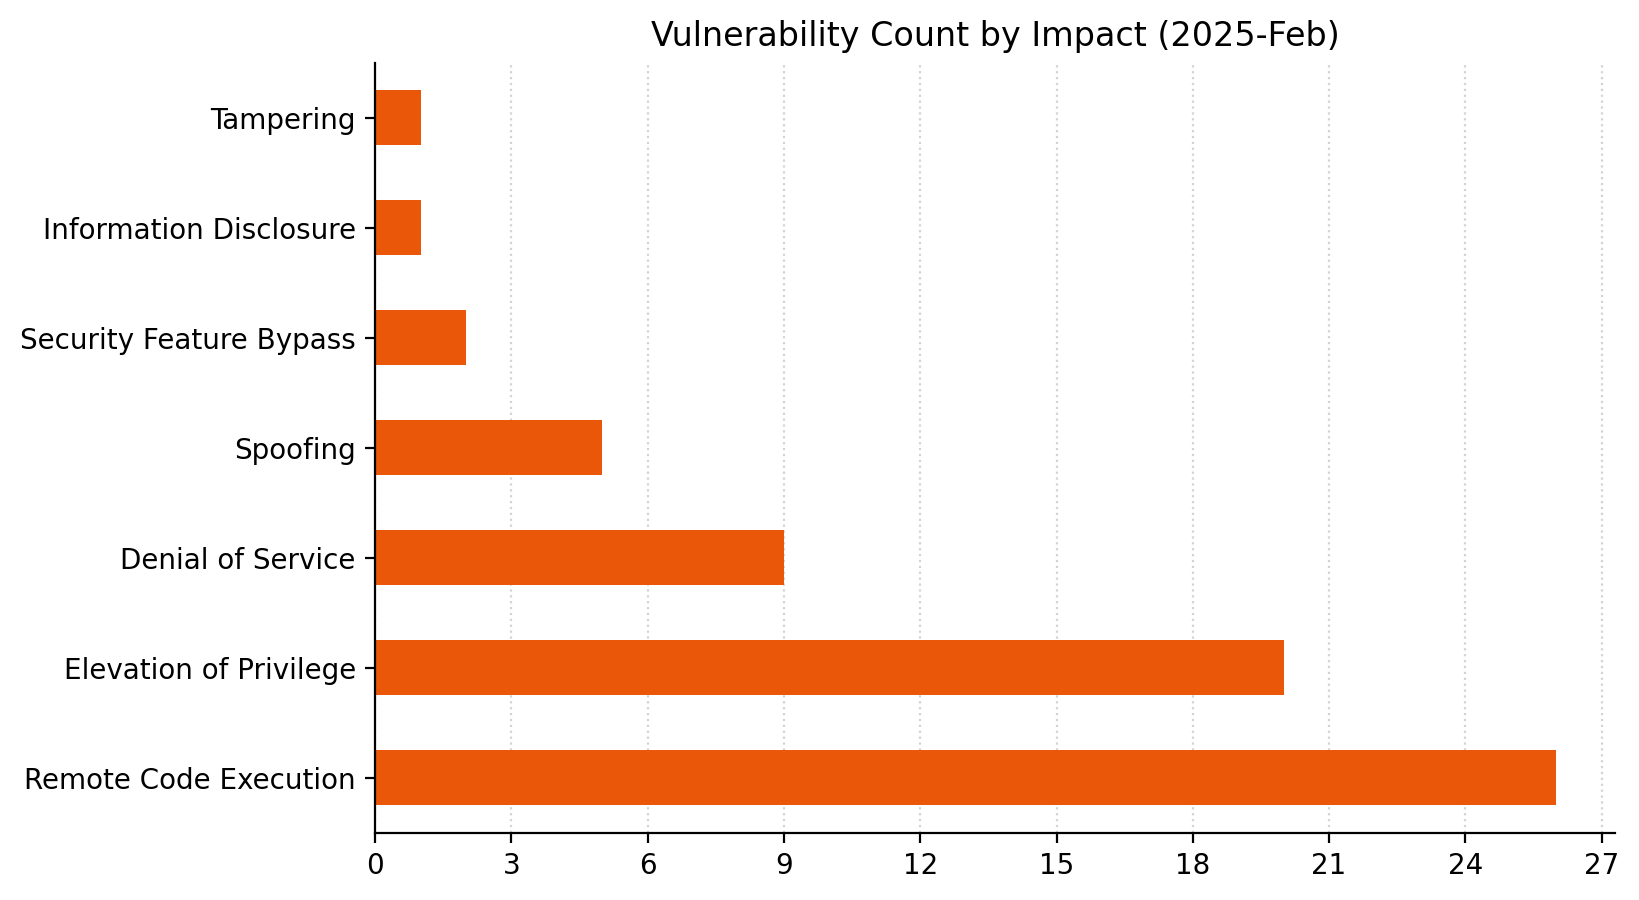
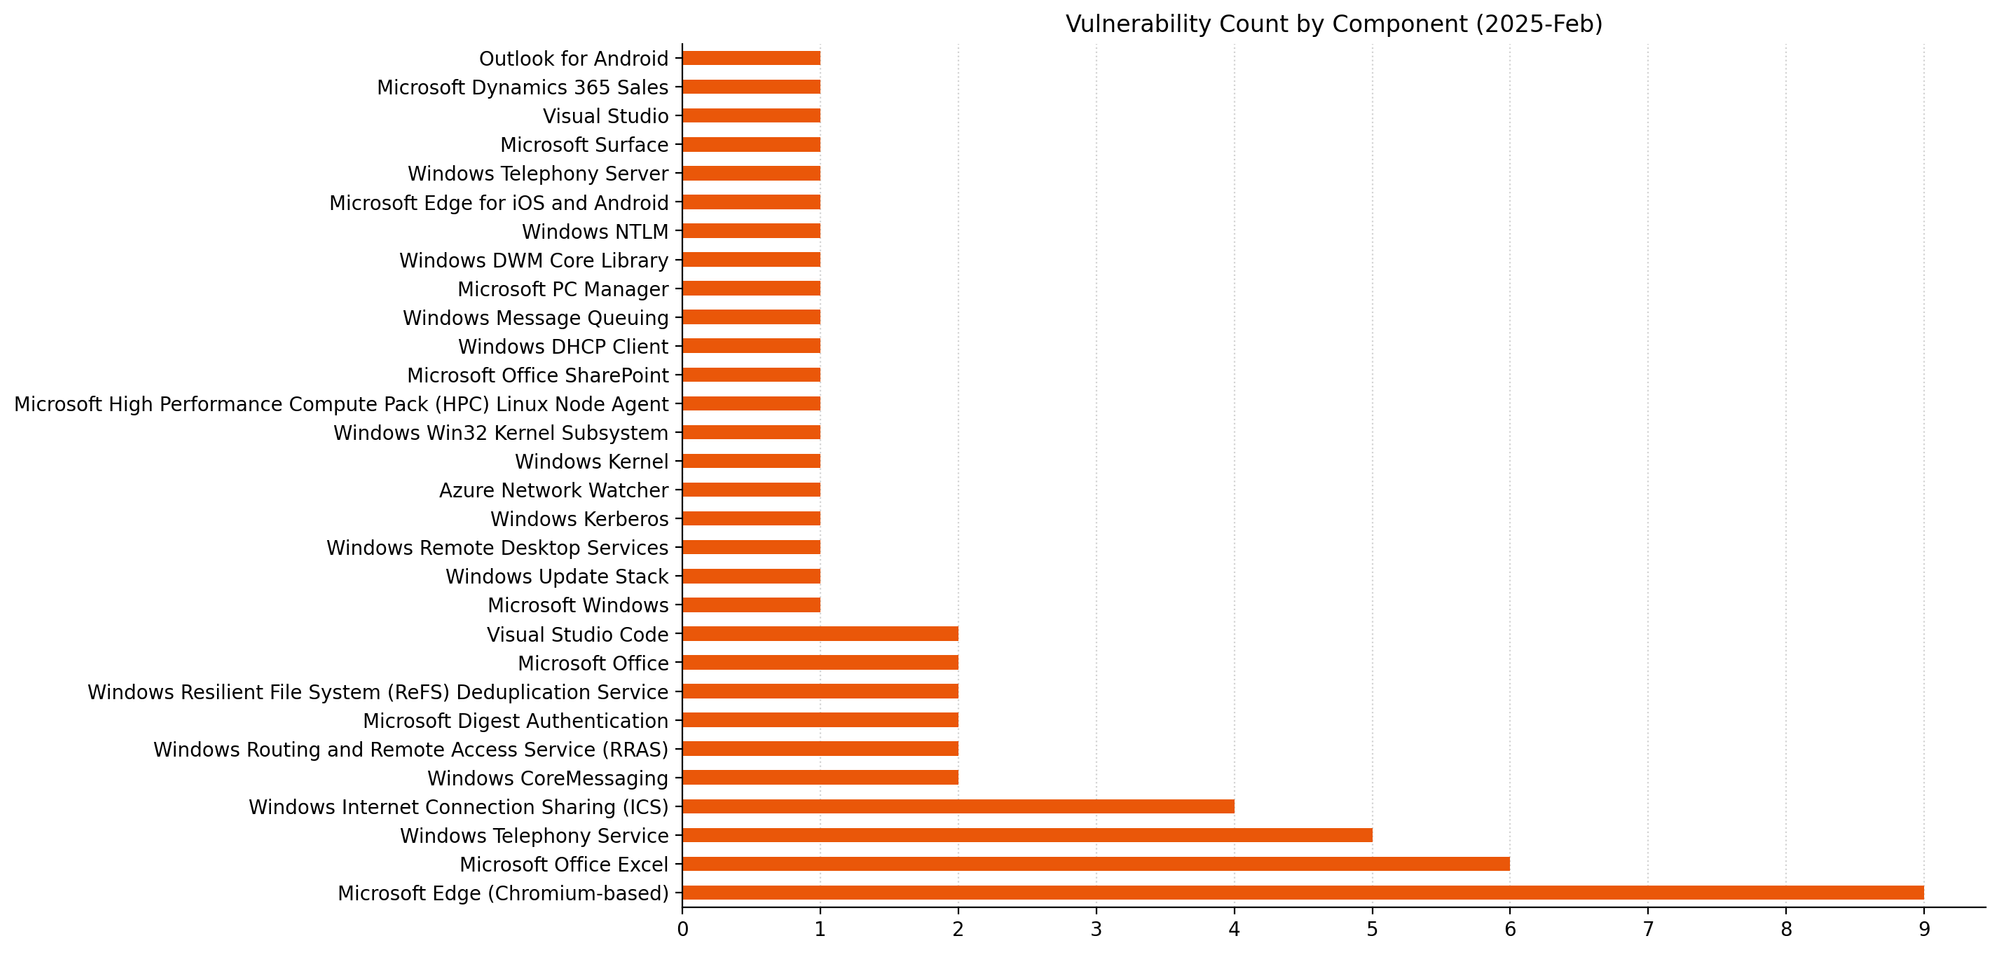
Microsoft is addressing 56 vulnerabilities this February 2025 Patch Tuesday. Microsoft has evidence of in-the-wild exploitation for two of the vulnerabilities published today, which is reflected in CISA KEV. Microsoft is aware of public disclosure for two other vulnerabilities. This is now the fifth consecutive month where Microsoft has published zero-day vulnerabilities on Patch Tuesday without evaluating any of them as critical severity at time of publication. Today also sees the publication of just three critical remote code execution (RCE) vulnerabilities. Eleven browser vulnerabilities have already been published separately this month, and are not included in the total.
Ancillary Function Driver: zero-day EoP
All versions of Windows receive patches today for CVE-2025-21418, a heap-based buffer overflow in the Windows Ancillary Function Driver (AFD). Successful exploitation leads to SYSTEM privileges. The AFD has been around for decades; it handles foundational networking functionality, so it is necessarily a kernel driver which interacts with a great deal of user-supplied input. It is perhaps not very shocking that AFD has been the site of a significant number of problems over the years: specifically, elevation of privilege (EoP) vulnerabilities. Microsoft is aware of existing exploitation in the wild, and with low attack complexity, low privilege requirements, and no requirement for user interaction, CVE-2025-21418 is one to prioritize for patching. The relatively low CVSSv3 base score of 7.8 and severity rating of Important may appear relatively mild; however, broad similarities exist between this vuln and CVE-2024-38193, which Rapid7 flagged as ripe for malware abuse on the day it was published, and which has subsequently been linked to exploitation by North Korean state-associated threat actor tracked as Lazarus.
Windows Storage: zero-day EoP
Ever wanted to delete a file on a Windows box, but pesky permissions prevented you from achieving your goal? CVE-2025-21391 might be just what you need: an elevation of privilege (EoP) vulnerability in the Windows Storage service for which Microsoft is aware of exploitation in the wild. No user interaction is required, and attack complexity is low, and the weakness is given as “CWE-59: Improper Link Resolution Before File Access” but what are attackers hoping to achieve here? Although the advisory provides scant detail, and even offers some vague reassurance that “an attacker would only be able to delete targeted files on a system”, it would be a mistake to assume that the impact of deleting arbitrary files would be limited to data loss or denial of service. As long ago as 2022, ZDI researchers set out how a motivated attacker could parlay arbitrary file deletion into full SYSTEM access using techniques which also involve creative misuse of symbolic links.
NTLMv2 disclosure: zero-day spoofing
It’s almost surprising when any particular Patch Tuesday doesn’t involve plugging one or two holes through which NTLM hashes can leak. CVE-2025-21377 describes an NTLMv2 hash disclosure vulnerability where exploitation ultimately results in the attacker gaining the ability to authenticate as the targeted user. Minimal user interaction with a malicious file is required, including selecting, inspecting, or “performing an action other than opening or executing the file.” This trademark linguistic ducking and weaving may be Microsoft’s way of saying “if we told you any more, we’d give the game away.” Accordingly, Microsoft assesses exploitation as more likely. The advisory acknowledges researchers from 0patch by ACROS Security — who also reported last month’s NTLM hash disclosure zero-day vuln CVE-2025-21308 — as well as others from Securify and Cathay Pacific; this might be the first instance of an airline receiving credit for reporting a Microsoft zero-day vulnerability.
Surface: zero-day container escape
A wide array of Microsoft Surface machines are vulnerable to CVE-2025-21194 until patched, although the most recent Surface Pro 10 and 11 series are not listed as vulnerable. The vulnerability is described as a security feature bypass, and exploitation could lead to container escape from a UEFI host machine and compromise of the hypervisor. Surface devices receive updates via Windows Update, although the advisory also gives brief instructions for users who wish to apply the updates manually. Microsoft describes the vulnerability as publicly disclosed.
LDAP server: critical RCE
Any security advisory which lists multiple weakness types typically describes a complex vulnerability, and Windows LDAP critical remote code execution (RCE) CVE-2025-21376 is no exception. Successful exploitation requires an attacker to navigate multiple challenges, including winning a race condition. The prize: code execution on the Windows LDAP server. Although Microsoft seldom specifies the privilege level of code execution on LDAP server vulnerabilities, Rapid7 has noted previously that the LDAP service runs in a SYSTEM context, and that is the only safe assumption. All versions of Windows receive a patch.
DHCP client: critical RCE
Today sees the publication of a slightly mysterious critical RCE in the Windows DHCP Client Service. Exploitation of CVE-2025-21379 requires an attacker to intercept and potentially modify communications between the Windows DHCP client and the requested resource, which implies either that an attacker can break encryption, or that no encryption is present in the DHCP communication; this risk is highlighted in Microsoft’s own spec for DHCP implementation.
Excel: critical RCE
As if spreadsheets weren’t dangerous enough by themselves, today sees publication of CVE-2025-21381, a critical RCE in Excel. As usual for this class of attack, the advisory clarifies that “remote” in this case refers to the location of the attacker, since user interaction is required, and the code execution will be in the context of the user on their local machine. The Outlook Preview Pane is an attack vector, so simply glancing at an email containing a specially crafted malicious spreadsheet is enough for the attack to succeed, although an attacker could also convince a user to download and open a file from a website, or perhaps simply drop a few USB sticks in the parking lot.
Microsoft lifecycle update
In Microsoft product lifecycle news, SQL Server 2019 moves from mainstream support to extended support on 2025-02-28.
Rapid7 is investigating two separate events affecting Fortinet firewall customers:
Zero-day exploitation of CVE-2024-55591, an authentication bypass vulnerability in FortiOS and FortiProxy disclosed earlier this week. Successful exploitation could allow remote attackers to gain super-admin privileges via crafted requests to the Node.js websocket module.
A January 15, 2025 dark web post from a threat actor who looks to have published IPs, passwords, and configuration data from 15,000 FortiGate firewalls. The data leaked online appears to be several years old (2022). Rapid7 has not attributed any CVEs to the leaked data at this time.
FortiGate data leak
On Wednesday, January 15, 2025, a threat actor named “Belsen Group” published a trove of Fortinet FortiGate firewall data on the dark web, allegedly from 15,000 organizations. The data released included IP addresses, passwords, and firewall configuration information — a potentially significant risk for organizations whose data was leaked.
Security researcher Kevin Beaumont has an initial analysis of the leaked data, along with his assessment that the data leaked this week appears to be from 2022. After conducting our own outreach to potentially affected organizations, Rapid7 has also confirmed that at least some of the leaked data originated from 2022 incidents where customer firewalls were compromised. Based on Beaumont’s analysis and observations from our own investigations, it’s likely that the data dump published by the threat actor contains primarily or entirely older data.
Rapid7 has not attributed the data leak to a specific CVE at this time. Beaumont said his observations from incident responses indicate that CVE-2022-40684 (a Fortinet firewall zero-day flaw from 2022) may have been the initial access vector that allowed for the large-scale firewall data leak.
New Fortinet zero-day CVE also exploited in the wild
Separately, on Tuesday, January 14, 2025, Fortinet disclosed CVE-2024-55591, a new zero-day vulnerability affecting FortiOS and FortiProxy. Security firm Arctic Wolf had previously published a blog on threat activity targeting Fortinet firewall management interfaces exposed to the public internet, saying that “a zero-day vulnerability is likely” but an initial access vector had not been confirmed. According to Arctic Wolf, the campaign “involved unauthorized administrative logins on management interfaces of firewalls, creation of new accounts, SSL VPN authentication through those accounts, and various other configuration changes.”
Fortinet’s advisory for CVE-2024-55591 includes indicators of compromise (IOCs) and notes that the vulnerability was reported as exploited in the wild at time of disclosure. No individual or firm is explicitly credited for discovering the vulnerability in Fortinet’s advisory, and Fortinet has not confirmed that CVE-2024-55591 is the zero-day vulnerability Arctic Wolf speculated was being leveraged threat activity.
Rapid7 MDR threat hunters have observed activity from IP addresses publicly attributed to the threat campaign targeting CVE-2024-55591, but our team has so far only noted connections consistent with scanning or reconnaissance activity and not exploitation.
Zero-day vulnerabilities in Fortinet FortiOS, the operating system that runs on FortiGate firewalls, have been a relatively common occurrence in recent years and have been leveraged in a wide range of financially motivated, state-sponsored, and other attacks. In addition to CVE-2024-55591, prominent FortiOS zero-day flaws have included:
CVE-2018-13379, while not a zero-day, was disclosed in 2019 and allowed attackers to download SSL-VPN system files and steal credentials. It was consistentlyexploited in the years following disclosure despite a wide range of warnings and publicly available information on known threat activity.
Like CVE-2022-40684, CVE-2024-55591 is an authentication bypass using an alternate path or channel (CWE-288). While it does not currently appear likely that CVE-2024-55591 is the vulnerability that enabled the collection and release of FortiGate firewall configuration data on January 15, 2025, the vulnerability is nevertheless being exploited in the wild and should be treated with urgency.
Mitigation guidance
According to Fortinet’s advisory, the following products and versions are vulnerable to CVE-2024-55591:
Fortinet FortiOS 7.0.0 through 7.0.16 (fixed in 7.0.17 or above)
Fortinet FortiProxy 7.2.0 through 7.2.12 (fixed in 7.2.13 or above)
Fortinet FortiProxy 7.0.0 through 7.0.19 (fixed in 7.0.20 or above)
Per Fortinet, other versions of FortiOS (6.4, 7.2, 7.4, 7.6) and FortiProxy (2.0, 7.4, 7.6) are not affected. Customers should update to a fixed version immediately, without waiting for a regular patch cycle to occur, and review Fortinet’s IOCs to aid investigations into suspicious activity. Indicators include examples of administrative or local users added by adversaries.
Customers should also ensure that firewall management interfaces are not exposed to the public internet and limit IP addresses that can reach administrative interfaces. If your organization was impacted by the January 15, 2025 FortiGate firewall data leak, you should change administrative and local user passwords immediately. FortiOS also supports multi-factor authentication (MFA) for local user accounts, which Rapid7 strongly recommends implementing.
Rapid7 customers
InsightVM and Nexpose customers can assess their exposure to CVE-2024-55591 with vulnerability checks available in the January 15, 2025 content release. Customers already have coverage for all other FortiOS vulnerabilities mentioned in this blog from past content releases.
Microsoft is addressing 161 vulnerabilities this January 2025 Patch Tuesday. Microsoft has evidence of in-the-wild exploitation and/or public disclosure for eight of the vulnerabilities published today, with three listed on CISA KEV. This is now the fourth consecutive month where Microsoft has published zero-day vulnerabilities on Patch Tuesday without evaluating any of them as critical severity at time of publication. Today also sees the publication of nine critical remote code execution (RCE) vulnerabilities. Unusually, Microsoft has not yet published any browser vulnerabilities this month.
Access: triple zero-day RCE
Today sees the publication of three very similar zero-day Microsoft Access vulnerabilities: CVE-2025-21366, CVE-2025-21395, and CVE-2025-21186. In each case, Microsoft notes public disclosure, but does not claim evidence of exploitation in the wild. Successful exploitation leads to code execution via heap-based buffer overflow, and requires that an attacker convince the user to download and open a malicious file.
Curiously, in each case, one portion of the advisory FAQ describes the update protection as “blocking potentially malicious extensions from being sent in an email”, but the remainder of the advisory doesn’t clarify how this would prevent malicious activity. Typically, patches provide protection by blocking malicious files upon receipt of a malicious email attachment, rather than preventing a malicious attachment from being sent in the first place, since an attacker is free to send whatever they like from any system they control.
The FAQ does mention that users who would otherwise have interacted with a malicious attachment will instead receive a notification that there was an attachment but “it cannot be accessed”, which is perhaps the best play on words we’ve seen from MSRC in a while.
Hyper-V NT Kernel Integration VSP: triple zero-day EoP
Microsoft is addressing a trio of related Windows Hyper-V NT Kernel Integration VSP elevation of privilege vulnerabilities today: CVE-2025-21333, CVE-2025-21334, and CVE-2025-21335. Microsoft is aware of exploitation in the wild for all three, as seen on both the Microsoft advisories and CISA KEV. In each case, exploitation leads to SYSTEM privileges. The advisories are short on additional detail, beyond a brief acknowledgement of Anonymous — presumably an undisclosed party, rather than the hacktivist collective — on CVE-2025-21333.
While we can sometimes infer context from prior examples, in this case there aren’t any; there is no mention of Hyper-V NT Kernel Integration VSP in any vulnerability published by Microsoft, at least as far back as 2017. If we look back five years, CVE-2020-16885 does describe an elevation of privilege vulnerability in the Windows storage VSP driver, but there isn’t a lot to go on there either.
The Virtualization Service Provider (VSP) resides in the root partition of a Hyper-V instance, and provides synthetic device support to child partitions over the Virtual Machine Bus (VMBus): it’s the foundation of how Hyper-V allows the child partition to trick itself into thinking that it’s a real computer. Given that the entire thing is a security boundary, it’s perhaps surprising that no Hyper-V NT Kernel Integration VSP vulnerabilities have been acknowledged by Microsoft until today, but it won’t be at all shocking if more now emerge.
The advisories published today do not clarify whether the elevation of privilege is only to SYSTEM within the child partition, but container escape specialists will surely be hunting for exploits in this area.
Windows Themes: zero-day NTLM disclosure
Many enterprise users or even admins may not think about Windows Themes very often, but consider CVE-2025-21308: a spoofing vulnerability where successful exploitation leads to improper disclosure of an NTLM hash, which allows an attacker to impersonate the user from whom it was acquired. Microsoft does not have evidence of in-the-wild exploitation, but does note public disclosure.
The advisory FAQ dances around the exploitation methodology without explaining; what we learn is that once an attacker had somehow delivered a malicious file to the target system, a user would need to manipulate the malicious file, but not necessarily click or open it. Without further detail, we can only speculate, but it’s plausible that simply opening a folder containing the file in Windows Explorer — including the Downloads folder — or inserting a USB drive, would be enough to trigger the vulnerability and see your NTLM hash leak silently for collection by the threat actor.
Some good news: Microsoft has removed NTLMv1 support from Windows 11 24H2 and Server 2025 onwards. Less good: it has been a whole two months since Microsoft last patched a zero-day NTLM disclosure vulnerability; that flaw was within MSHTML/Trident, and Windows 11 24H2 and Server 2025 were still vulnerable, since NTLMv2 is still supported across the board.
On the advisory for CVE-2025-21308, Microsoft does link to documents describing a mitigation technique: restricting NTLM traffic. This is certainly worth a look, since a representative of reporting research organization 0patch has confirmed that NTLMv2 is affected by CVE-2025-21308.
Windows Installer: zero-day EoP
Installing or updating software often requires elevated privileges, and researchers and threat actors have known this for a long time. The advisory for CVE-2025-21275 doesn’t weigh us down with lengthy explanations, it simply says that successful exploitation leads to SYSTEM privileges. Microsoft is aware of public disclosure of this vulnerability, but not in-the-wild exploitation.
CVE-2025-21275 is the latest in a long line of Windows Installer elevation of privilege vulnerabilities; Microsoft has now published 37 Windows Installer elevation of privilege vulnerabilities in total since the start of 2020, although only five of those have been zero-days, with only CVE-2024-38014 known by Microsoft to have been exploited prior to publication in September 2024.
PGM: critical RCE
Microsoft’s in-house research teams are a reliable source of vulnerability discovery in Microsoft products, and today we get patches for the self-discovered CVE-2025-21307, a critical RCE in the Windows Reliable Multicast Transport Driver (RMCAST) with a CVSSv3 base score of 9.8. The vulnerability is only exploitable on a system where a program is listening on a Pragmatic General Multicast (PGM) port.
In 2025, you might very well expect that any service that a major commercial operating system exposes to the network would provide at least some form of authentication capability, but if so, prepare to be disappointed by the Windows implementation of PGM. The concept was first described in RFC 3208, which was published in 2001 in an Experimental state and stayed that way. As Microsoft themselves put it, “the PGM specification [RFC3208] is ambiguous in a number of areas”.
Given the lack of required user interaction and remote attack vector for CVE-2025-21307, it’s well worth asking yourself: does our firewall allow a PGM receiver to receive inbound traffic from the public internet? If so, the second-best time to prevent that is right now.
OLE: critical RCE
Outlook admins who force their users to read emails in plain text only can skip this paragraph, but everyone else should be aware of CVE-2025-21298, a Windows Object Linking and Embedding (OLE) critical RCE with a CVSSv3 base score of 9.8. The eternal threat of the malicious inbound email finds expression again here; just previewing the wrong email in Outlook is all it takes for an attacker to achieve code execution in the context of the user. All versions of Windows receive a patch.
On Wednesday, January 8, 2025, Ivanti disclosed two CVEs affecting Ivanti Connect Secure, Policy Secure, and Neurons for ZTA gateways. CVE-2025-0282 is a stack-based buffer overflow vulnerability that allows remote, unauthenticated attackers to execute code on the target device. CVE-2025-0283 is a stack-based buffer overflow that allows local authenticated attackers to escalate privileges on the device.
Ivanti’s advisory indicates that CVE-2025-0282 has been exploited in the wild against a limited number of Connect Secure devices. Per the vendor, Ivanti Policy Secure and Neurons for ZTA are not known to have been exploited in the wild at time of disclosure. Google’s Mandiant division and Microsoft’s Threat Intelligence Center (MSTIC) are credited with the discovery of the two issues, which almost certainly means further intelligence will be released soon on one or more zero-day threat campaigns targeting Ivanti devices.
Ivanti also has a short blog available on the new CVEs here.
Mitigation guidance
The following products and versions are vulnerable to CVE-2025-0282:
Ivanti Connect Secure 22.7R2 through 22.7R2.4
Ivanti Policy Secure 22.7R1 through 22.7R1.2
Ivanti Neurons for ZTA 22.7R2 through 22.7R2.3
The following products and versions are vulnerable to CVE-2025-0283:
Ivanti Connect Secure 22.7R2.4 and prior, 9.1R18.9 and prior
Ivanti Policy Secure 22.7R1.2 and prior
Ivanti Neurons for ZTA 22.7R2.3 and prior
Ivanti has a full table of affected versions and corresponding solution estimates in its advisory. As of 1 PM ET on Wednesday, January 8, patches are available for both CVEs in Ivanti Connect Secure (22.7R2.5), but the CVEs are unpatched in Ivanti Policy Secure and Neurons for ZTA (patches appear to be expected January 21, 2025, per the advisory).
Customers should apply available Ivanti Connect Secure patches immediately, without waiting for a typical patch cycle to occur. Ivanti’s advisory notes that “Exploitation of CVE-2025-0282 can be identified by the Integrity Checker Tool (ICT). We strongly advise all customers to closely monitor their internal and external ICT as a part of a robust and layered approach to cybersecurity to ensure the integrity and security of the entire network infrastructure.”
For the latest information, please refer to the vendor advisory.
Rapid7 customers
Our VM engineering team is researching options for coverage of CVE-2025-0282 and CVE-2025-0283 in Ivanti Connect Secure and expects vulnerability checks to be available to InsightVM and Nexpose customers no later than Thursday, January 9, 2025.
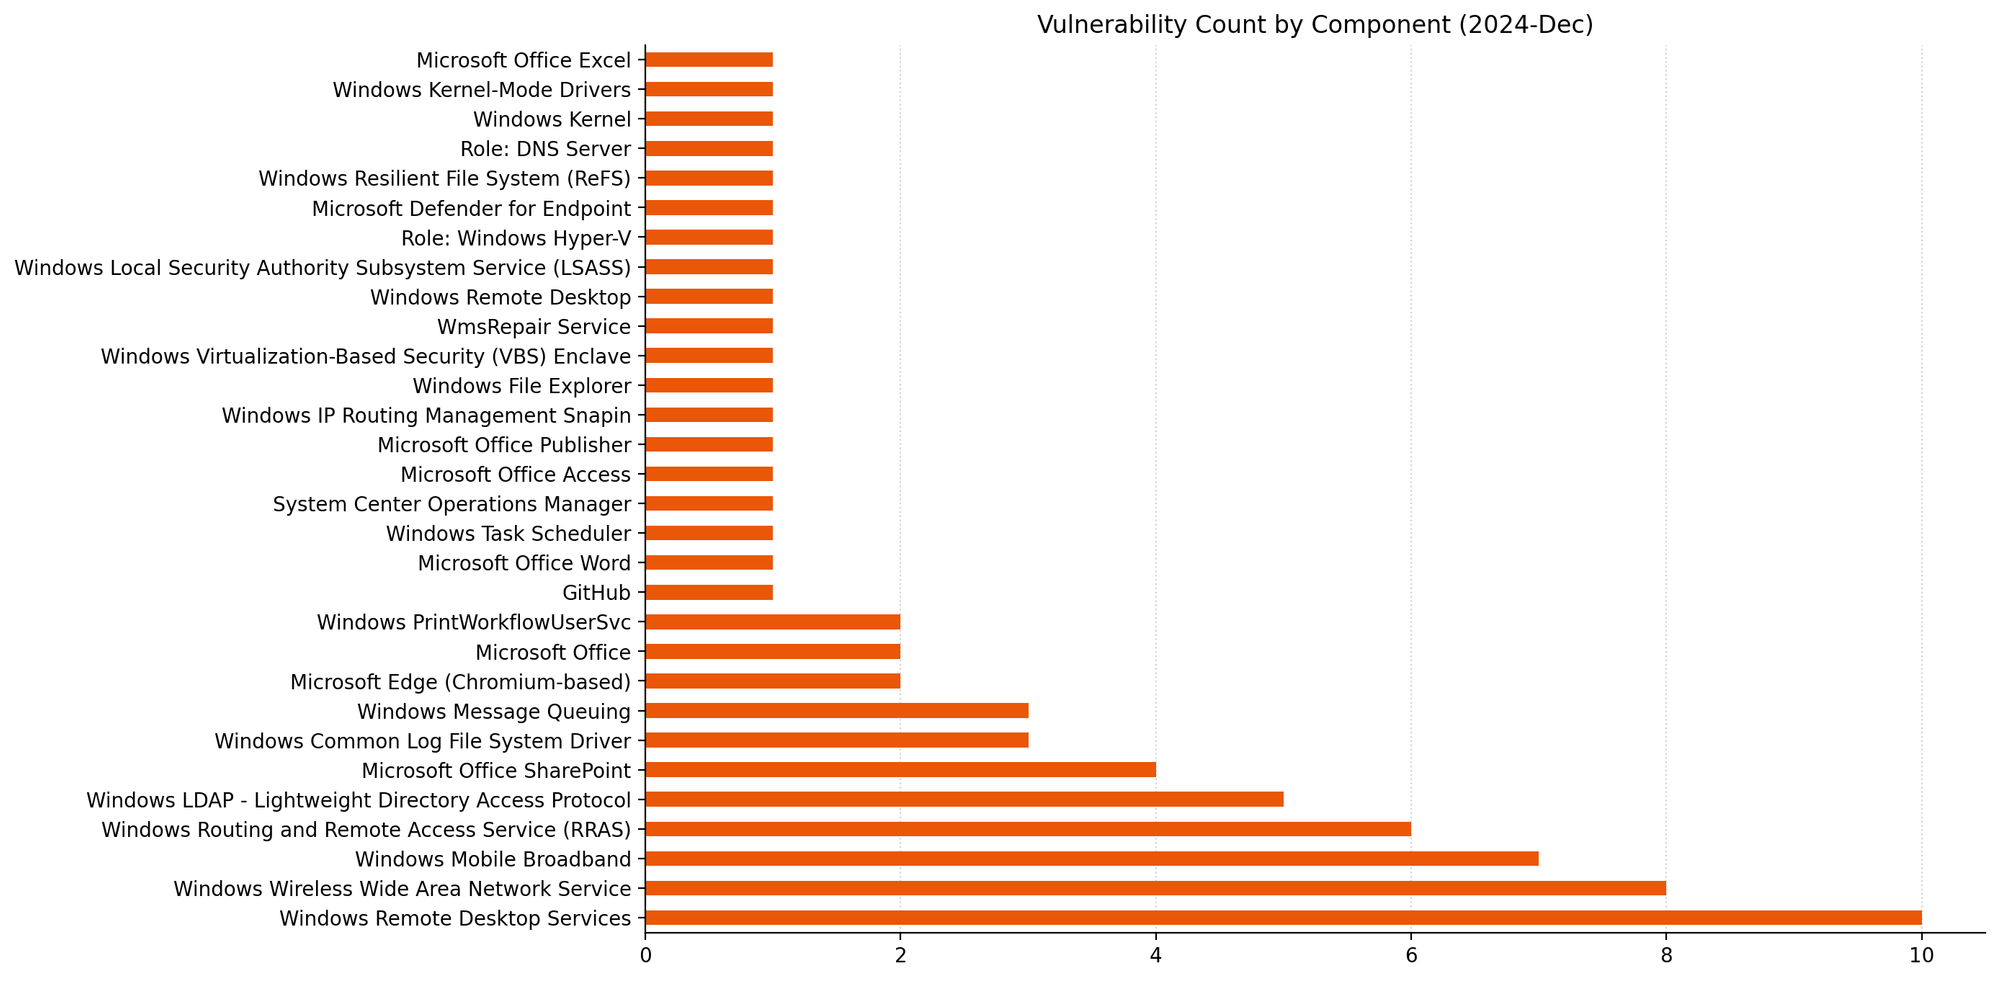
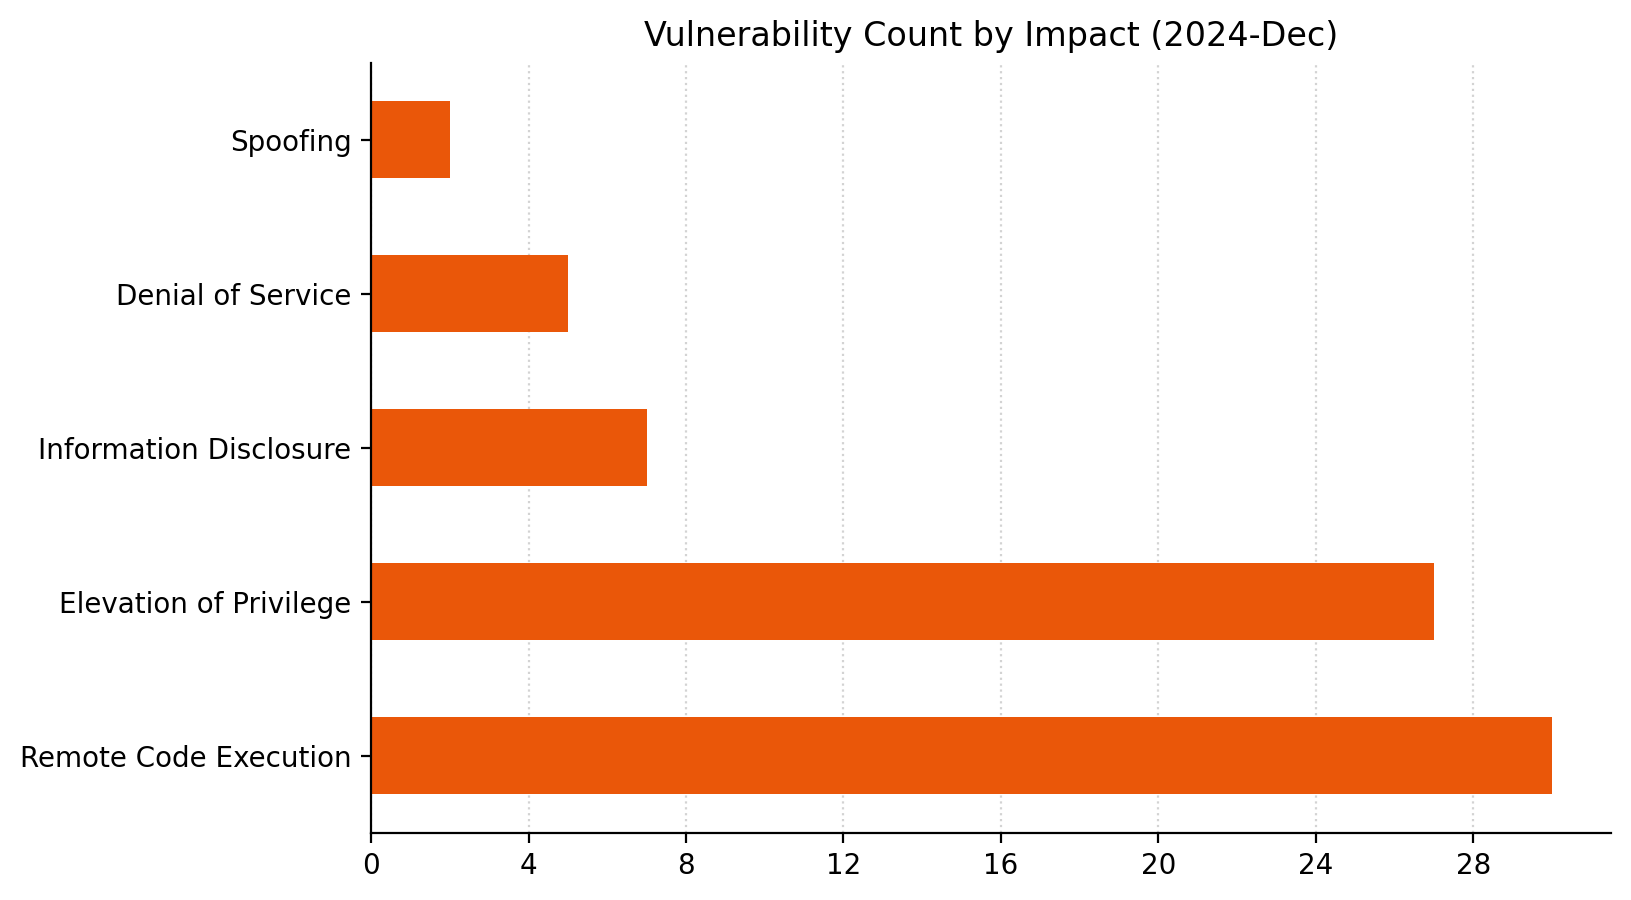
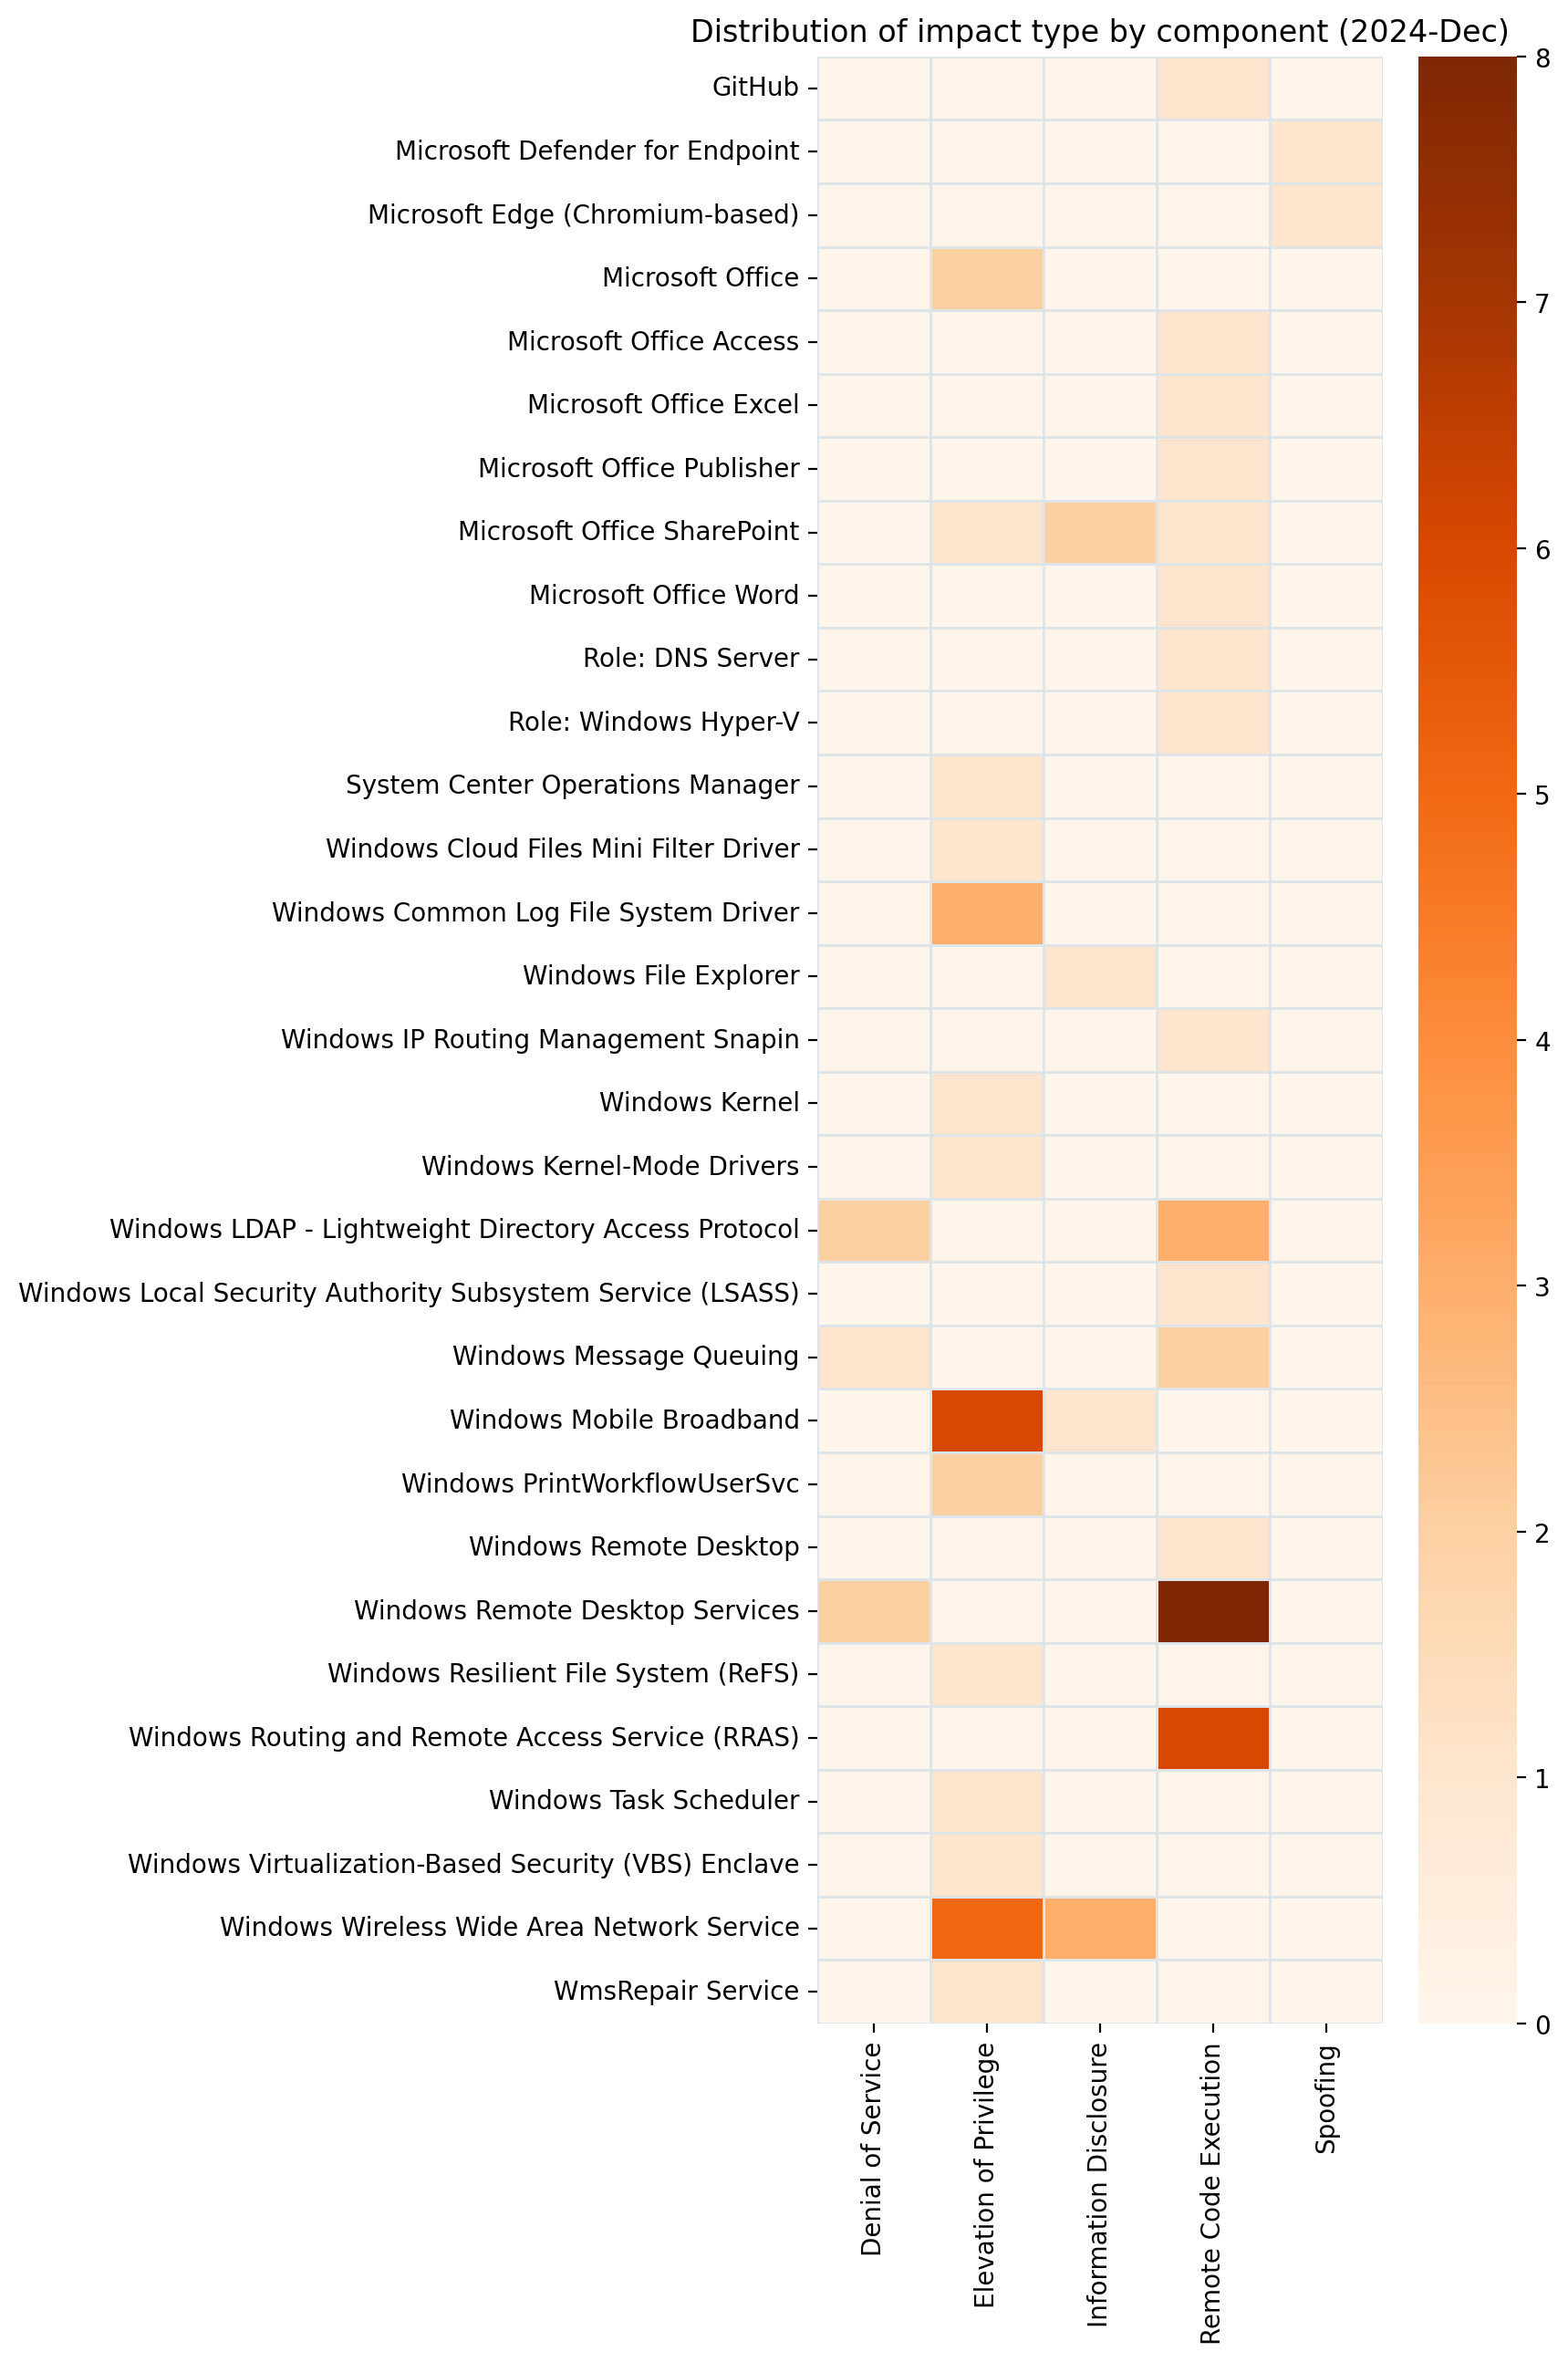
Microsoft is addressing 70 vulnerabilities this December 2024 Patch Tuesday. Microsoft has evidence of in-the-wild exploitation and public disclosure for one of the vulnerabilities published today, and this is reflected in a CISA KEV entry. For the third month in a row, Microsoft has published zero-day vulnerabilities on Patch Tuesday without evaluating any of them as critical severity at time of publication. Today sees the publication of 16 critical remote code execution (RCE) vulnerabilities, which is more than usual. Two browser vulnerabilities have already been published separately this month, and are not included in the total.
Common Log File System: zero-day EoP
This month’s zero-day vulnerability is CVE-2024-49138, an elevation of privilege vulnerability in the Windows Common Log File System (CLFS) driver, a general-purpose Windows logging service that can be used by software clients running in user-mode or kernel-mode. Exploitation leads to SYSTEM privileges, and if this all sounds familiar, it should.
There have been a series of zero-day elevation of privilege vulnerabilities in CLFS over the past few years. Past offenders are CVE-2022-24521, CVE-2023-23376, CVE-2022-37969, and CVE-2023-28252; today’s addition of CVE-2024-49138 is the first CLFS zero-day vulnerability which Microsoft has published in 2024. Although the advisory doesn’t provide much detail on the means of exploitation, the weakness is CWE-122: Heap-based Buffer Overflow, which most commonly leads to crashes/denial of service, but can also lead to code execution.
Ransomware authors who have abused previous CLFS vulnerabilities will be only too pleased to get their hands on a fresh one. Expect more CLFS zero-day vulnerabilities to emerge in the future, unless Microsoft decides to perform a full replacement of the aging CLFS codebase instead of offering spot fixes for specific flaws. Patches are available for all versions of Windows.
Groups of critical RCE
Patterns emerge when we consider the 16 critical RCE vulnerabilities published today as a whole, which might somewhat reduce the level of alarm that unusually large number might otherwise cause weary defenders.
LDAP: critical RCE
A trio of Windows LDAP critical RCE vulnerabilities receive patches this month, including CVE-2024-49112, which has a CVSSv3 base score of 9.8, which is the highest of any of the vulnerabilities which Microsoft has published today. Exploitation is via a specially crafted set of LDAP calls, and leads to code execution within the context of the LDAP service; although the advisory doesn’t specify, the LDAP service runs in a SYSTEM context. Microsoft advises defenders who still permit domain controllers to receive inbound RPC calls from untrusted networks or to access the internet to stop doing that.
LSASS: critical RCE
Another potential cause for concern this month: CVE-2024-49126 is a critical RCE in the Local Security Authority Subsystem Service (LSASS). Exploitation could potentially be carried out remotely, and the attacker needs no privileges, nor does the user need to perform any action; the only silver lining is that an attacker must win a race condition. Although the advisory says that code execution would be in the context of the server’s account, it might be safest to assume that code execution would be in a SYSTEM context.
Hyper-V: container escape
CVE-2024-49117 describes a container escape for Hyper-V; exploitation requires that the attacker make specially crafted file operation requests on the virtual machine (VM) to hardware resources on the VM, which could result in remote code execution on the hypervisor. The FAQ on the advisory sets out that no special privileges are required in the context of the VM, so any level of access is enough to break free from the VM. We also learn that the container escape could be lateral, where an attacker moves from one VM to another, rather than to the hypervisor.
Remote Desktop Services: 8 critical RCEs
All eight critical RCE vulnerabilities in Remote Desktop Services published today (e.g. CVE-2024-49106) share a number of similarities: they have identical CVSS vectors, exploitation requires that an attacker win a race condition, and the same research group is credited in each case.
Microsoft lifecycle update
There are no significant Microsoft product lifecycle transitions this month.
On Monday, December 9, multiple security firms began privately circulating reports of in-the-wild exploitation targeting Cleo file transfer software. Late the evening of December 9, security firm Huntress published a blog on active exploitation of three different Cleo products (docs):
Cleo VLTrader, a server-side solution for “mid-enterprise organizations”
Cleo Harmony, which provides file transfer capabilities for “large enterprises”
Cleo LexiCom, a desktop-based client for communication with major trading networks
Huntress’s blog says the exploitation they’re seeing across Cleo products results from an insufficient patch for CVE-2024-50623, a vulnerability disclosed in Cleo VLTrader, Cleo Harmony, and Cleo LexiCom in October 2024. Cleo indicated that the vulnerability was fixed in version 5.8.0.21 of all three solutions, but according to Huntress, 5.8.0.21 remains vulnerable to exploitation. CVE-2024-50623 is a cross-site scripting issue (CWE-79) that allows for unauthenticated remote code execution on target systems.
Update: Cleo evidently communicated with customers on December 10 acknowledging a “critical vulnerability in Cleo Harmony, VLTrader, and LexiCom that could allow an unauthenticated user to import and execute arbitrary bash or PowerShell commands on the host system by leveraging the default settings of the Autorun directory.”
As of December 10, Rapid7 MDR has confirmed successful exploitation of this issue in customer environments; similar to Huntress, our team has observed enumeration and post-exploitation activity and is investigating multiple incidents.
File transfer software continues to be a target for adversaries, and for financially motivated threat actors in particular. Rapid7 recommends taking emergency action to mitigate risk related to this threat.
Mitigation guidance
The following products and versions are vulnerable to CVE-2024-50623. The information below contradicts previous vendor guidance, which indicated that 5.8.0.21 resolved the issue. Cleo has updated their advisory as of December 10, 2024 to confirm 5.8.0.21 is still vulnerable.
Cleo Harmony before and including version 5.8.0.21
Cleo VLTrader before and including version 5.8.0.21
Cleo LexiCom before and including version 5.8.0.21
According to Huntress, “Cleo is preparing a new CVE designation and expects a new patch to be released mid-week.”
In the absence of an effective patch for CVE-2024-50623 (and any other CVEs that may be assigned to this exploit), Cleo customers should remove affected products from the public internet, ensuring they are behind a firewall. Per Huntress’s investigation, disabling Cleo’s Autorun Directory, which allows command files to be automatically processed, may also prevent the latter part of the attack chain from being executed.
Huntress’s blog has several descriptions of post-exploitation activity, including attack chain artifacts, commands run, and files dropped for persistence. Rapid7 recommends that affected customers review these indicators and investigate their environments for suspicious activity dating back to at least December 3, 2024.
Rapid7 customers
InsightVM and Nexpose customers will be able to assess their exposure to CVE-2024-50623 on Windows with an authenticated vulnerability check expected to be available in today’s (Tuesday, December 10) content release. Please note that content releases are typically available late in the evening ET on Patch Tuesday.
InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of rules deployed and alerting on behavior related to this threat:
Suspicious Process – XORed Data in PowerShell
Suspicious Process – PowerShell System.Net.Sockets.TcpClient
Attacker Behavior – Possible Cleo MFT Exploitation 2024
Wowza Streaming Engine below v4.9.1 is vulnerable to multiple vulnerabilities on Linux and Windows. An unauthenticated attacker can poison the Wowza Streaming Engine Manager web dashboard with a stored cross-site scripting (“XSS”) payload. When an administrator views the poisoned dashboard, additional authenticated vulnerabilities will automatically be exploited for remote code execution on the underlying server. The code execution context is privileged: root on Linux, LocalSystem on Windows. These vulnerabilities are tracked as CVE-2024-52052, CVE-2024-52053, CVE-2024-52054, CVE-2024-52055, and CVE-2024-52056. All five were patched on November 20, 2024, with the release of Wowza Streaming Engine v4.9.1.
Product description
Wowza Streaming Engine is media server software used by many organizations for livestream broadcasts, video on-demand, closed captioning, and media system interoperability. The Wowza Streaming Engine Manager component is a web application, and it’s used to manage and monitor Wowza Media Server instances. At the time of publication, approximately 18,500 Wowza Streaming Engine servers are exposed to the public internet, and many of those systems also expose the Manager web application.
Credit
These issues were reported to the Wowza Media Systems team by Ryan Emmons, Lead Security Researcher at Rapid7. The vulnerabilities are being disclosed in accordance with Rapid7’s vulnerability disclosure policy. Rapid7 is grateful to the Wowza team for their assistance and collaboration.
Vulnerability details
The testing target was Wowza Streaming Engine v4.8.27+5, the latest version available at the time of research. Rapid7 identified multiple security vulnerabilities as part of this research project, and those vulnerabilities are outlined in the table below.
CVE
Description
CVSS
CVE-2024-52052
An authenticated administrator can define a custom application property and poison a stream target for high-privilege remote code execution.
Exploitation was tested against Wowza Streaming Engine on two different operating systems: Ubuntu Linux 22.04.1 and Windows Server 2022. Based on information provided by the vendor, the unauthenticated injection vulnerability affects all Wowza Streaming Engine Manager versions, while the four authenticated vulnerabilities were introduced in v4.3.0.
Vendor statement
“We at Wowza Media Systems are focused on security excellence, and by partnering with trusted researchers like Rapid7, we proactively respond to and fix vulnerabilities to safeguard our customers’ interests.”
Mitigation guidance
Per to the vendor, issues in this disclosure can be remediated by upgrading to Wowza Streaming Engine version 4.9.1 or any future version.
Rapid7 customers
InsightVM and Nexpose customers will be able to assess their exposure to CVE-2024-52052, CVE-2024-52053, CVE-2024-52054, CVE-2024-52055, and CVE-2024-52056 with authenticated vulnerability checks expected to be available in the November 20, 2024 content release.
Disclosure timeline
July 30, 2024 – September 3, 2024: Rapid7 attempts to contact the vendor to disclose vulnerabilities discovered in Wowza Streaming Engine. September 3, 2024: Rapid7 makes contact with the vendor, who acknowledges disclosure materials. September 5, 2024 – September 18, 2024: Rapid7 and vendor discuss coordinated vulnerability disclosure steps and timeline. October 2, 2024: Vendor communicates Q4 remediation timeline. October 31, 2024: Patch shared with Rapid7 for testing. November 4, 2024: Rapid7 confirms the patch is successful. November 5, 2024: Rapid7 provides CVE IDs. November 15, 2024: Vendor proposes Wednesday, November 20 for coordinated vulnerability disclosure. Rapid7 agrees. November 20, 2024: This disclosure.
On Friday, November 8, 2024, cybersecurity firm Palo Alto Networks (PAN) published a bulletin (PAN-SA-2024-0015) advising firewall customers to take steps to secure their firewall management interfaces amid unverified rumors of a possible new vulnerability. Rapid7 threat intelligence teams have also been monitoring rumors of a possible zero-day vulnerability, but until now, those rumors have been unsubstantiated.
Late in the evening of Thursday, November 14, the Palo Alto Networks advisory was updated to note that PAN had “observed threat activity exploiting an unauthenticated remote command execution vulnerability against a limited number of firewall management interfaces which are exposed to the Internet.” The firm indicated they are actively investigating. As of the morning of Friday, November 15, there is no CVE or fix for the issue PAN has identified.
Per the vendor bulletin:
Risk of exploitation is currently believed to be limited if access to the management interface access is restricted
No specific indicators of compromise (IOCs) are currently available
If the firewall management interface was exposed to the internet, PAN advises customers to monitor for suspicious threat activity (e.g., unrecognized configuration changes or users)
Prisma Access and Cloud NGFW are believed not to be affected, per the advisory; if this changes, Rapid7 will update this blog
Mitigation guidance
In lieu of a fix, Palo Alto Networks customers should ensure access to the firewall management interface is configured correctly in accordance with PAN’s recommended best practice deployment guidelines — namely, that access is restricted to trusted internal IPs only and the management interface is not exposedor accessible to the internet. More guidance is available here.
The Palo Alto Networks advisory also has directions on identifying internet-facing management interfaces and/or devices that may otherwise require remediation action. Rapid7 strongly recommends reviewing the advisory and configuration guidance. We will update this blog with further information as it becomes available, but as always, we encourage Palo Alto Networks customers to refer to the vendor advisory for the latest information.
Microsoft is addressing 90 vulnerabilities this November 2024 Patch Tuesday. Microsoft has evidence of in-the-wild exploitation and/or public disclosure for four of the vulnerabilities published today, although as with last month’s batch, it does not evaluate any of these zero-day vulnerabilities as critical severity (yet). Of those four, Microsoft lists two as exploited in the wild, and both of these are now listed on CISA KEV. Microsoft is aware of some level of public disclosure for three. Microsoft is also patching two further critical remote code execution (RCE) vulnerabilities today. Two browser vulnerabilities have already been published separately this month, and are not included in the total.
Active Directory Certificate Service: zero-day EoP aka EKUwu
CVE-2024-49019 describes an elevation of privilege vulnerability in Active Directory Certificate Services. While the vulnerability only affects assets with the Windows Active Directory Certificate Services role, an attacker who successfully exploits this vulnerability could gain domain admin privileges, so that doesn’t offer much comfort. Unsurprisingly, given the potential prize for attackers, Microsoft assesses future exploitation as more likely. Vulnerable PKI environments are those which include published certificates created using a version 1 certificate template with the source of subject name set to “Supplied in the request” and Enroll permissions granted to a broader set of accounts. Microsoft does not obviously provide any means of determining the certificate template version used to create a certificate, although the advisory does offer recommendations for anyone hoping to secure certificate templates.
There is a significant history of research and exploitation of Active Directory Certificate Services, including the widely-discussed Certified Pre-Owned series, and the discovering researchers have now added further to that corpus, tagging CVE-2024-49019 as ESC15. In keeping with another long-standing infosec tradition, the researcher has provided a fun celebrity vulnerability name — in this case, EKUwu, a portmanteau of EKU (Extended Key Usage) and UwU, an emoticon representing a cute face — as part of their detailed and insightful write-up.
MSHTML: zero-day NTLMv2 hash disclosure
Given the CVSSv3 base score of 6.0, one might almost be forgiven for overlooking CVE-2024-43451, which describes an NTLM hash disclosure spoofing vulnerability in the MSHTML platform which powered Internet Explorer. However, public disclosure and in-the-wild exploitation are always worth a look. Although exploitation requires that the user interact with a malicious file, a successful attacker receives the user’s NTLMv2 hash, and can then use that to authenticate as the user.
Microsoft has arguably scored CVE-2024-43451 correctly according to the CVSSv3.1 specification. However, although the Microsoft CVSSv3 vector describes an impact only to confidentiality, if an attacker can authenticate as the user post-exploitation, a further potential for subsequent impact to integrity and availability now exists; if we take that potential indirect effect into account, the CVSSv3 base score would look more like 8.8, which is the sort of number where alarm bells typically start ringing for many defenders. As a further sting in the tail, the advisory FAQ describes the required user interaction as minimal: left click, right click, or even the highly non-specific “performing an action other than opening or executing [the file]”. There’s certainly the potential for a long tail of exploitation here, especially in environments with more relaxed patching cadence.
The complete Windows catalog from Server 2025 and Windows 11 24H2 all the way back to Server 2008 receives patches for CVE-2024-43451. As Rapid7 has previously noted, MSHTML (also known as Trident) is still fully present in Windows — and unpatched assets are thus vulnerable — regardless of whether or not a Windows asset has Internet Explorer 11 disabled.
Exchange: zero-day sender spoofing
It’s been a few months since we’ve seen any security patches for Exchange, but the streak is now broken with a zero-day vulnerability. Mailserver admins should be paying attention to CVE-2024-49040, which is a publicly disclosed spoofing vulnerability. The specific weakness is CWE-451: User Interface (UI) Misrepresentation of Critical Information, which is often associated with phishing attacks, as well as browser vulnerabilities, and can describe a wide range of misdeeds, from visual truncation and UI overlay to homograph abuse. Microsoft does not yet claim knowledge of in-the-wild exploitation.
The advisory for CVE-2024-49040 hints that post-patching actions may be required for remediation of CVE-2024-49040, and links to further information in a separate article titled “Exchange Server non-RFC compliant P2 FROM header detection”. A careful read of the article doesn’t appear to list any mandatory post-patching actions; instead, there is an optional extra mitigation strategy action around Exchange Transport Rules, as well as an encouragingly detailed explanation of the protection offered by today’s patches. The article showcases that an Exchange-connected email client such as Outlook might display a forged sender as if it were legitimate, which we can all agree is not a good outcome. Attackers don’t have to look far to find other vulnerabilities to chain with this one, since today’s sibling zero-day vulnerability CVE-2024-43451 is certainly an option. On the other hand, let’s take a moment to appreciate the Exchange team’s blog title: “You Had Me at EHLO”.
Patches for CVE-2024-49040 are available for Exchange 2019 CU13 and CU14, as well as Exchange 2016 CU23. It’s worth remembering that both Exchange 2016 and 2019 have an extended end date of 2025-10-14, which is now less than a year away; this despite the fact that the successor for 2016 and 2019, which Microsoft is unsubtly branding as Exchange Server Subscription Edition, isn’t due for release until early in 2025 Q3. Many admins would no doubt prefer a longer upgrade window.
The researcher who reported CVE-2024-49040 also discovered a means to impersonate Microsoft corporate email accounts earlier this year, but went public with his findings after Microsoft dismissed his report; it appears that the relationship has been at least somewhat repaired.
Task Scheduler: zero-day EoP (but not SYSTEM)
Windows Task Scheduler facilitates all sorts of useful outcomes, and if you’re a threat actor, it now offers one more: elevation of privilege via CVE-2024-49039. Microsoft is aware of exploitation in the wild. Given the low attack complexity and low privileges requirement, no requirement for user interaction, high impact across the CIA triad, and changed scope, it’s no surprise that the CVSSv3 base score comes out as a relatively zesty 8.8. However, Windows elevation of privilege vulnerabilities are always most exciting for attackers when they lead directly to SYSTEM privileges, but that’s not the case here. The attacker in this scenario starts out in a low-privileged AppContainer sandbox, and exploitation via a malicious app provides medium integrity level privileges, which is the same as a regular non-administrative user on the system. Still, every step forward for a threat actor is a step back for defenders.
.NET: critical RCE
This month brings patches for CVE-2024-43498, a critical RCE in .NET 9.0 with a CVSSv3 base score of 9.8, which is so seldom a harbinger of good news. Exploitation might mean compromise of a desktop application by loading a malicious file, but most concerningly could also describe RCE in the context of a vulnerable .NET webapp via a specially crafted request. Microsoft assesses exploitation as less likely, but there’s nothing on the advisory which obviously supports that assessment, since this is a low-complexity network attack which requires neither privileges nor user interaction. CVE-2024-43498 is surely worthy of immediate patching. It’s also never a bad idea to review other options for protection, especially for internet-exposed services.
Kerberos: critical RCE
The advisory for CVE-2024-43639 describes a critical RCE in Kerberos with a CVSSv3 base score of 9.8, although not in great detail. The FAQ explains that an unauthenticated attacker could use a specially crafted application to leverage a cryptographic protocol vulnerability in Windows Kerberos to perform remote code execution against the target, but without providing much information about the target or the precise context of code execution. The only safe assumption here is that code execution is in a highly-privileged context on a server which handles key authentication tasks. Patch accordingly.
At the other end of the lifecycle continuum, .NET 6.0 receives its final scheduled updates today; as .NET 6.0 is/was a Long Term Support (LTS) version, and .NET 7.0 is already beyond end of life, the only current upgrade path is to .NET 8.0.
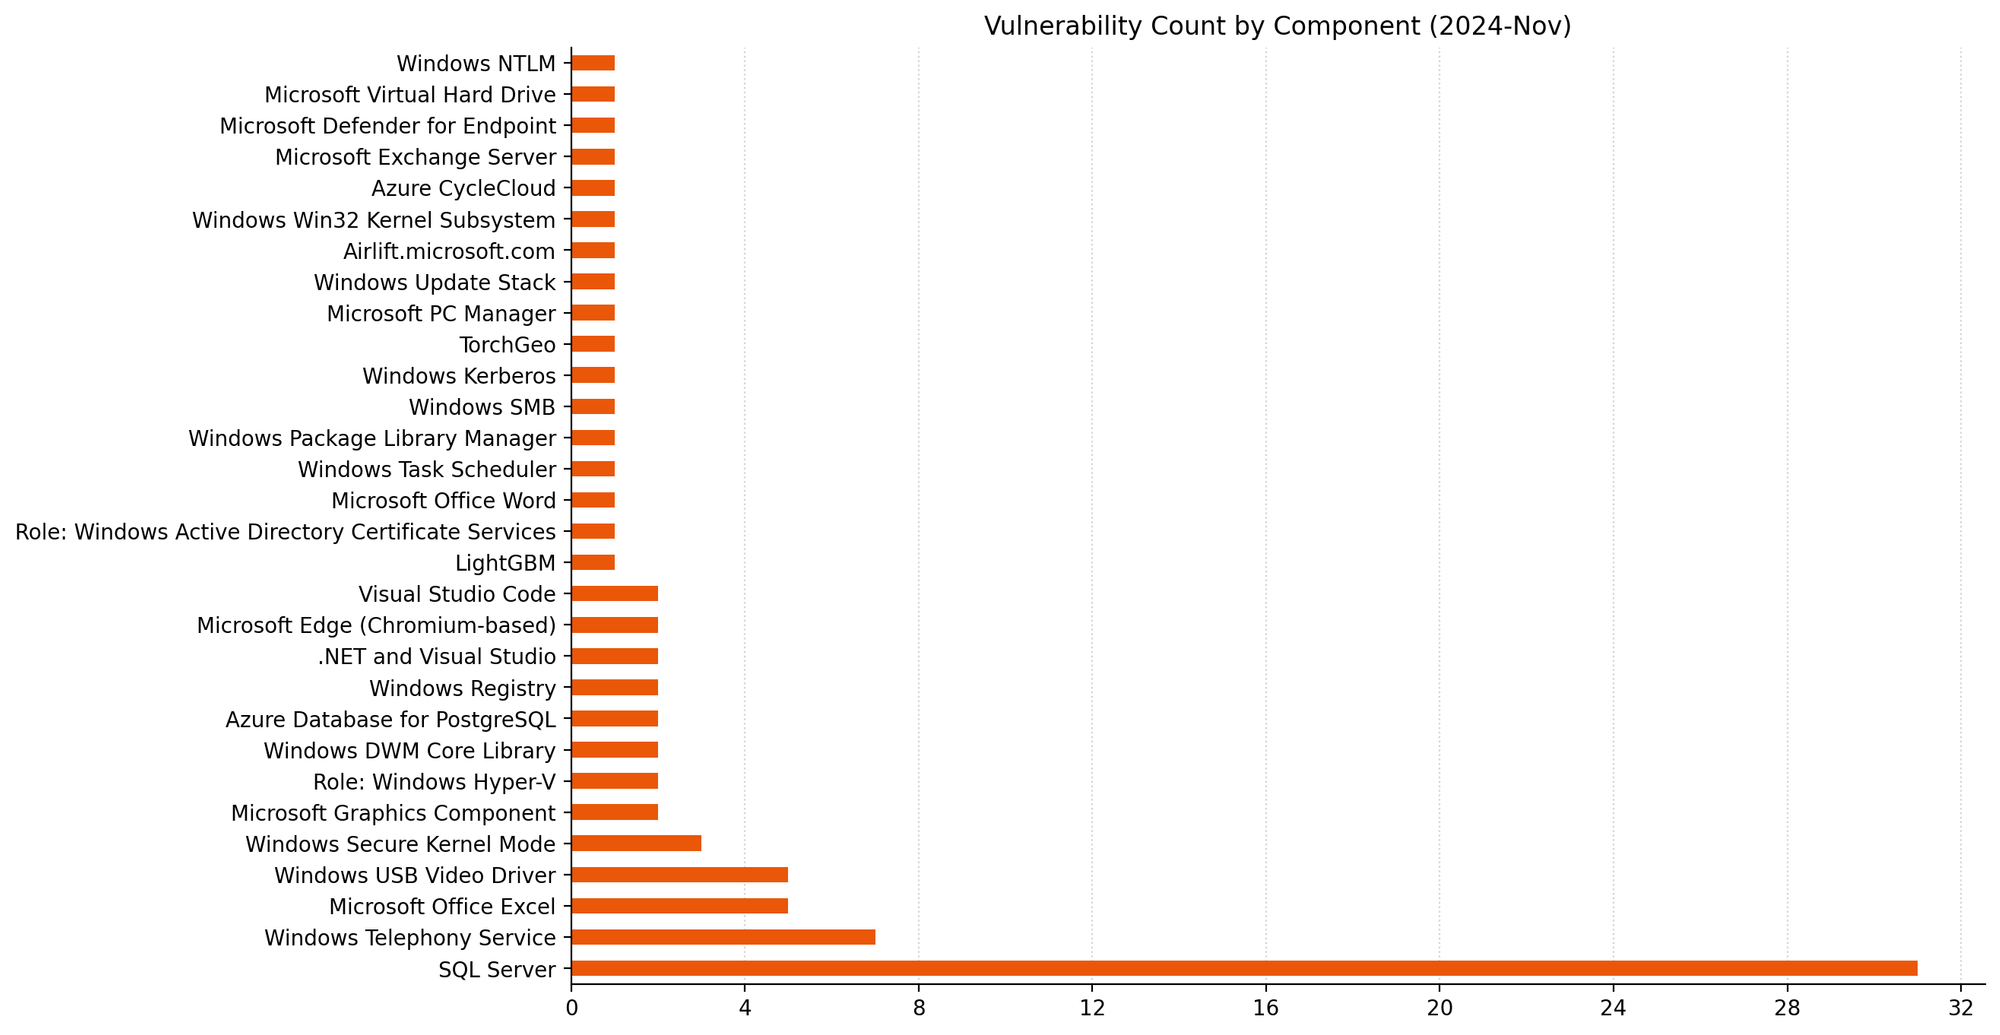
Summary charts
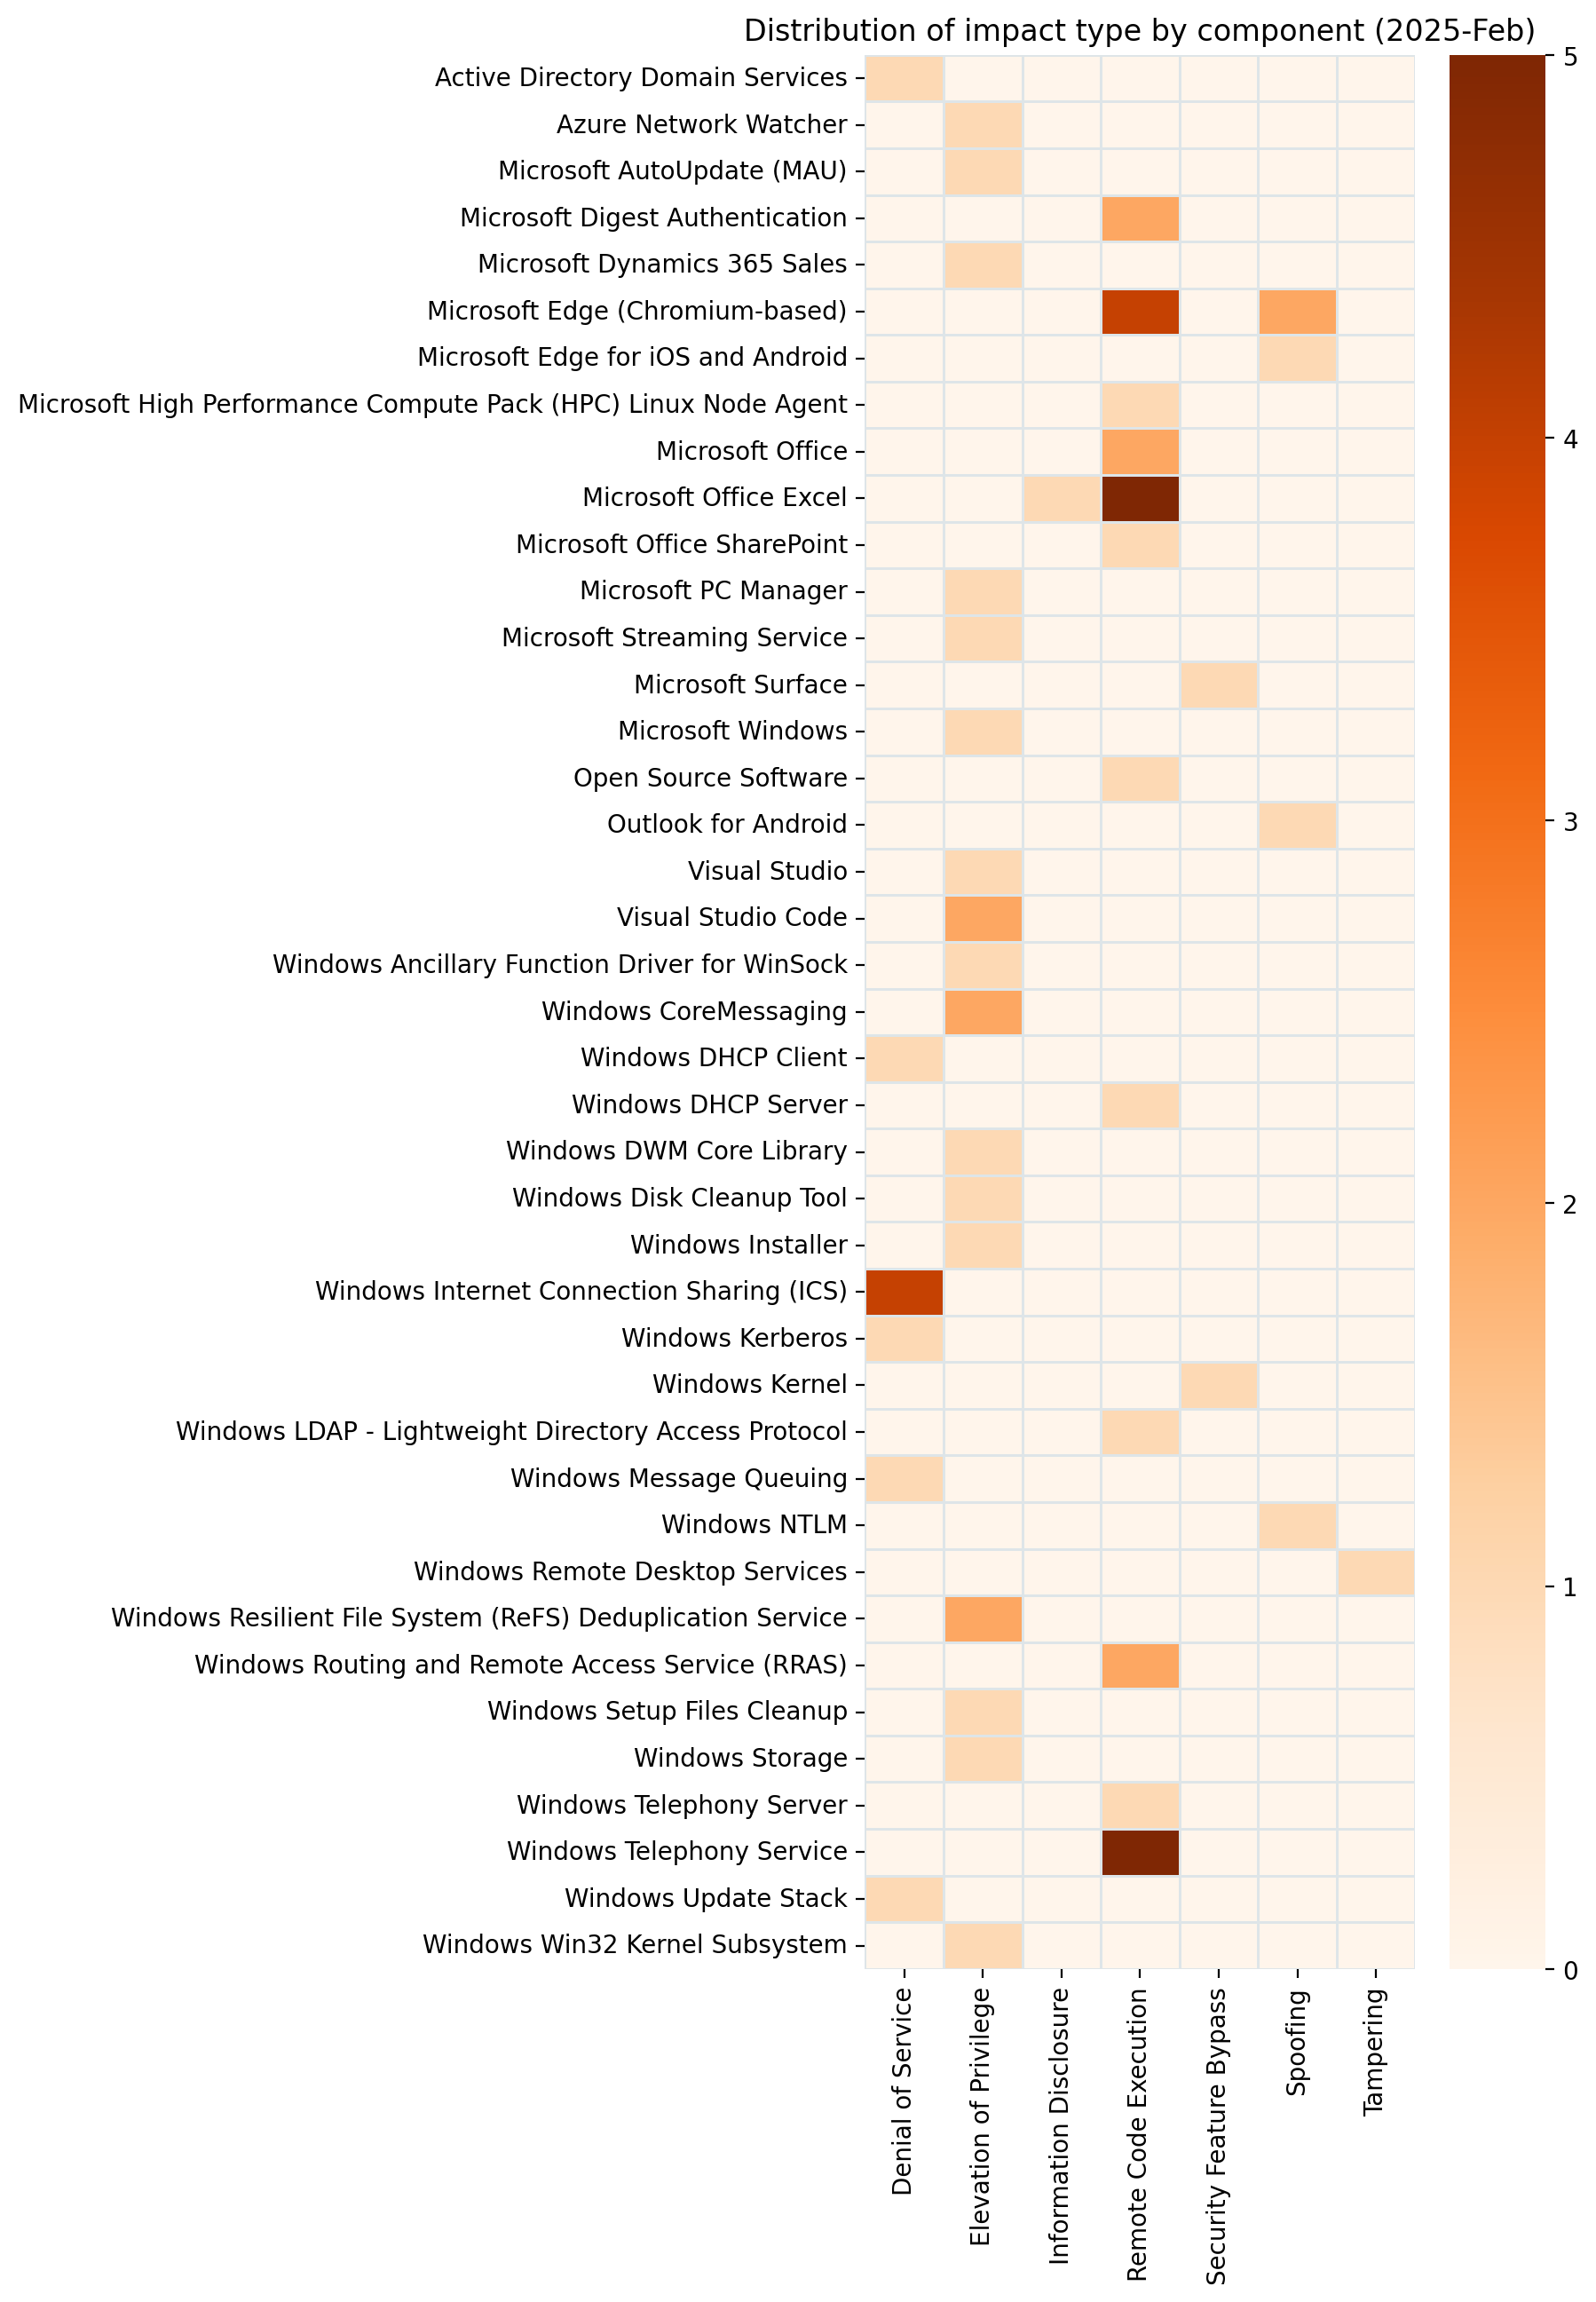
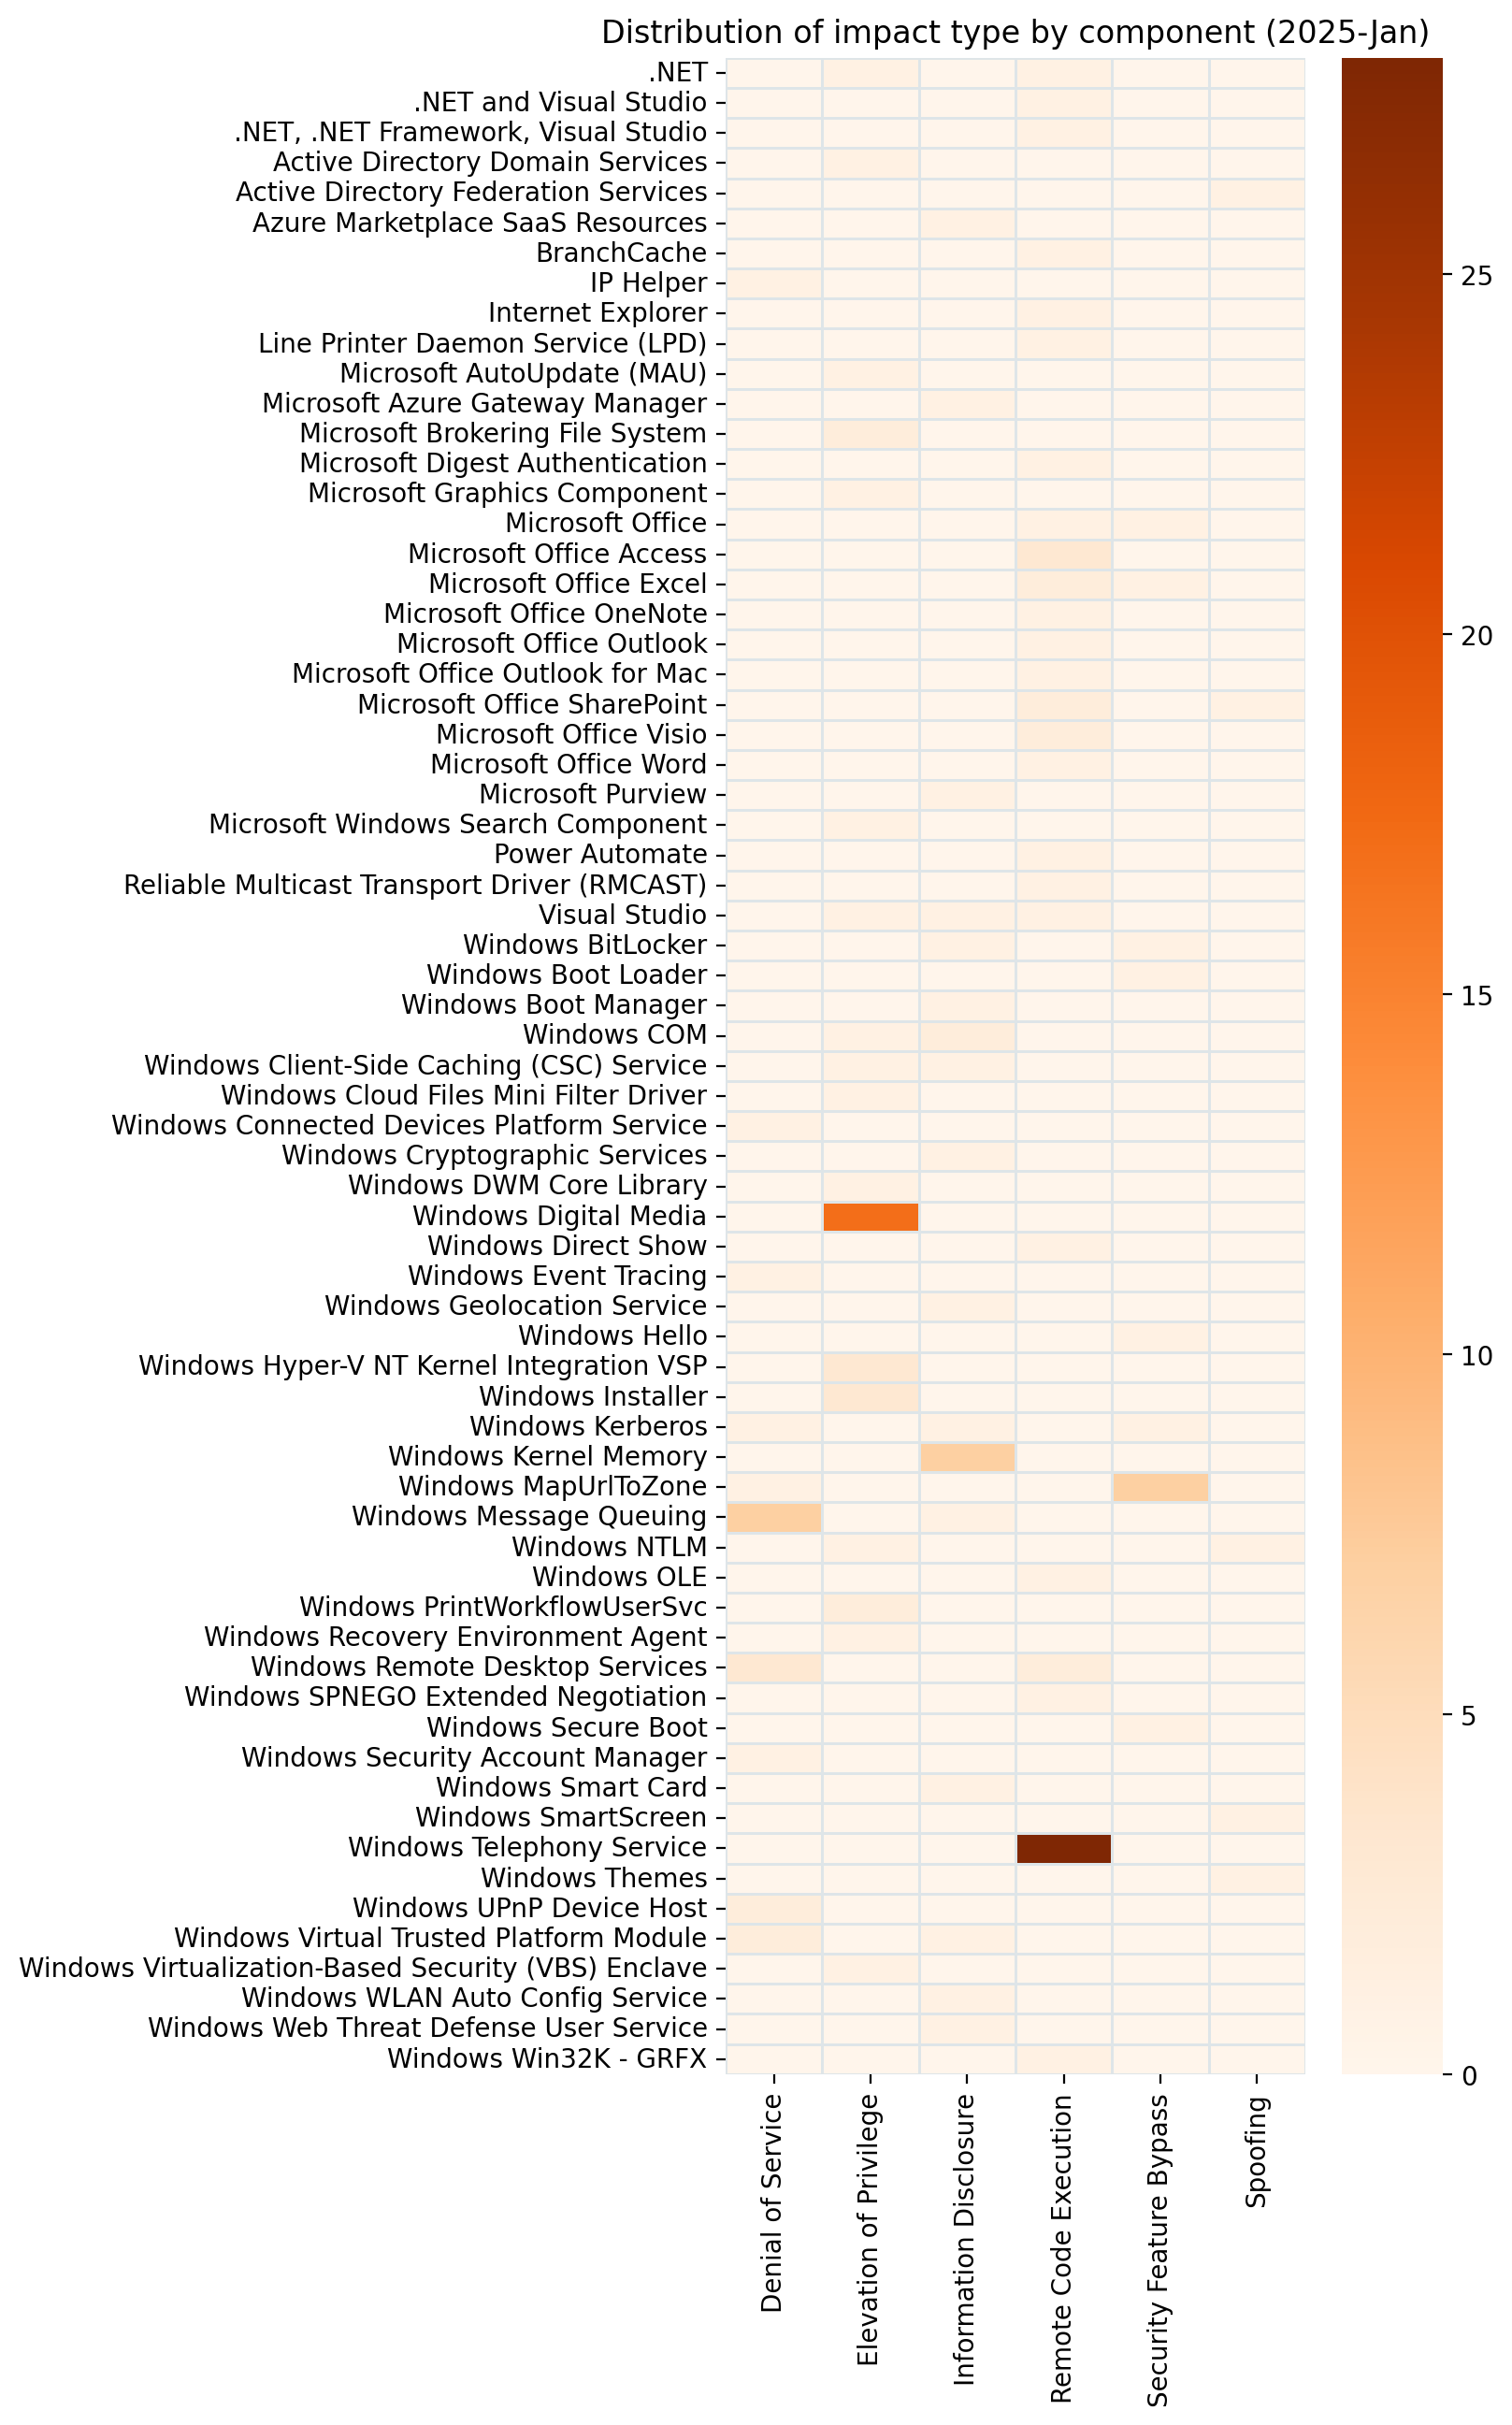
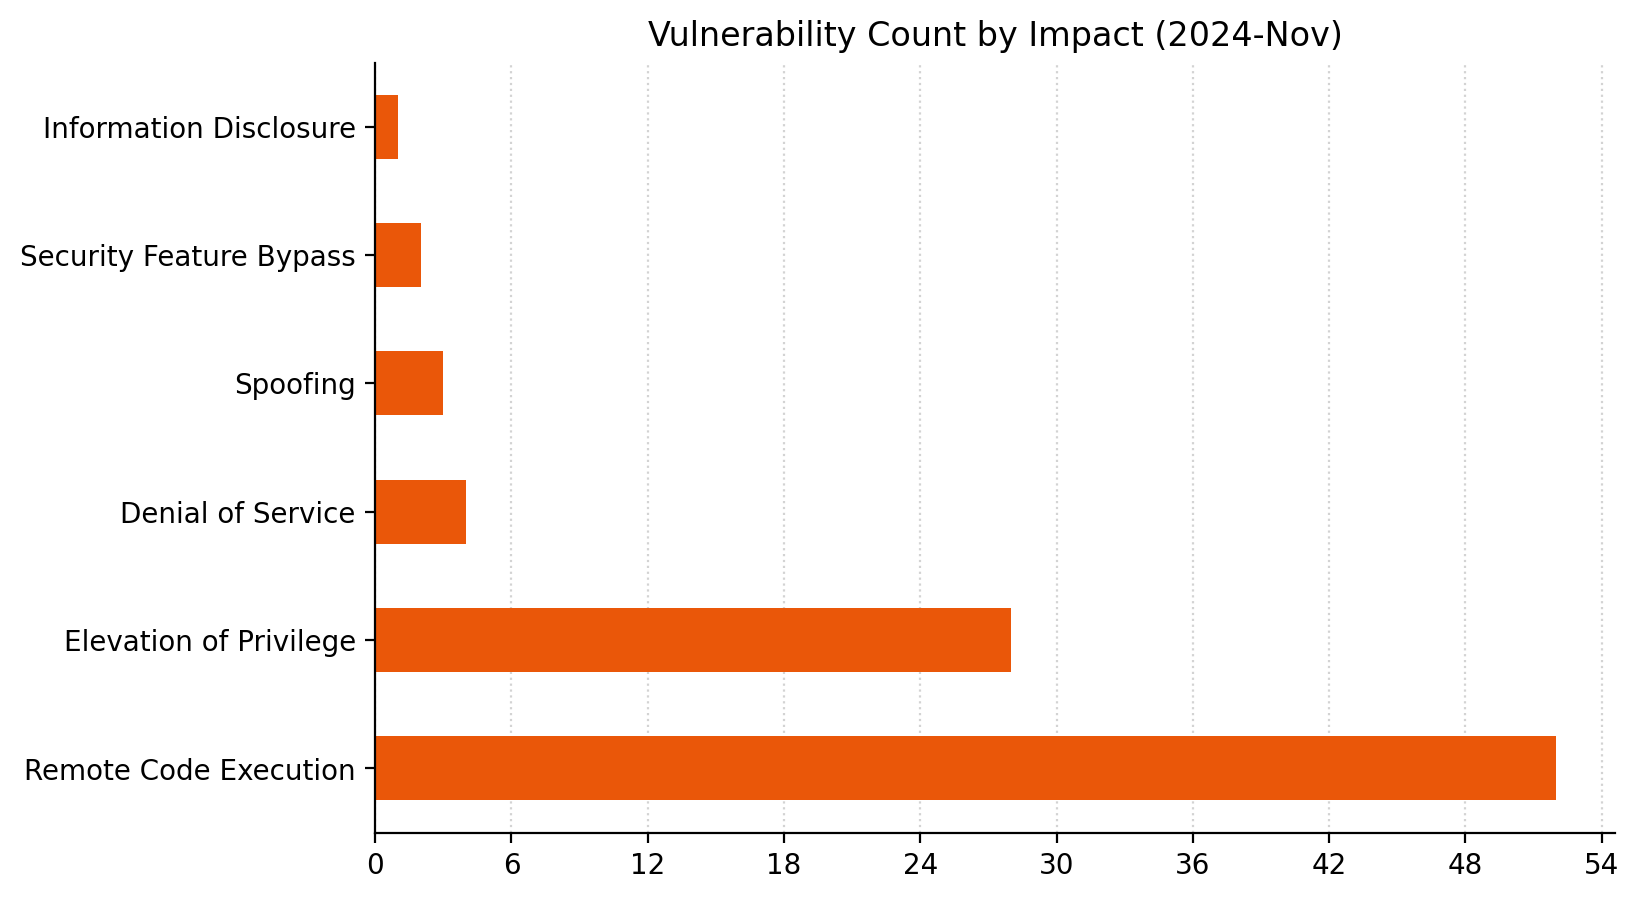
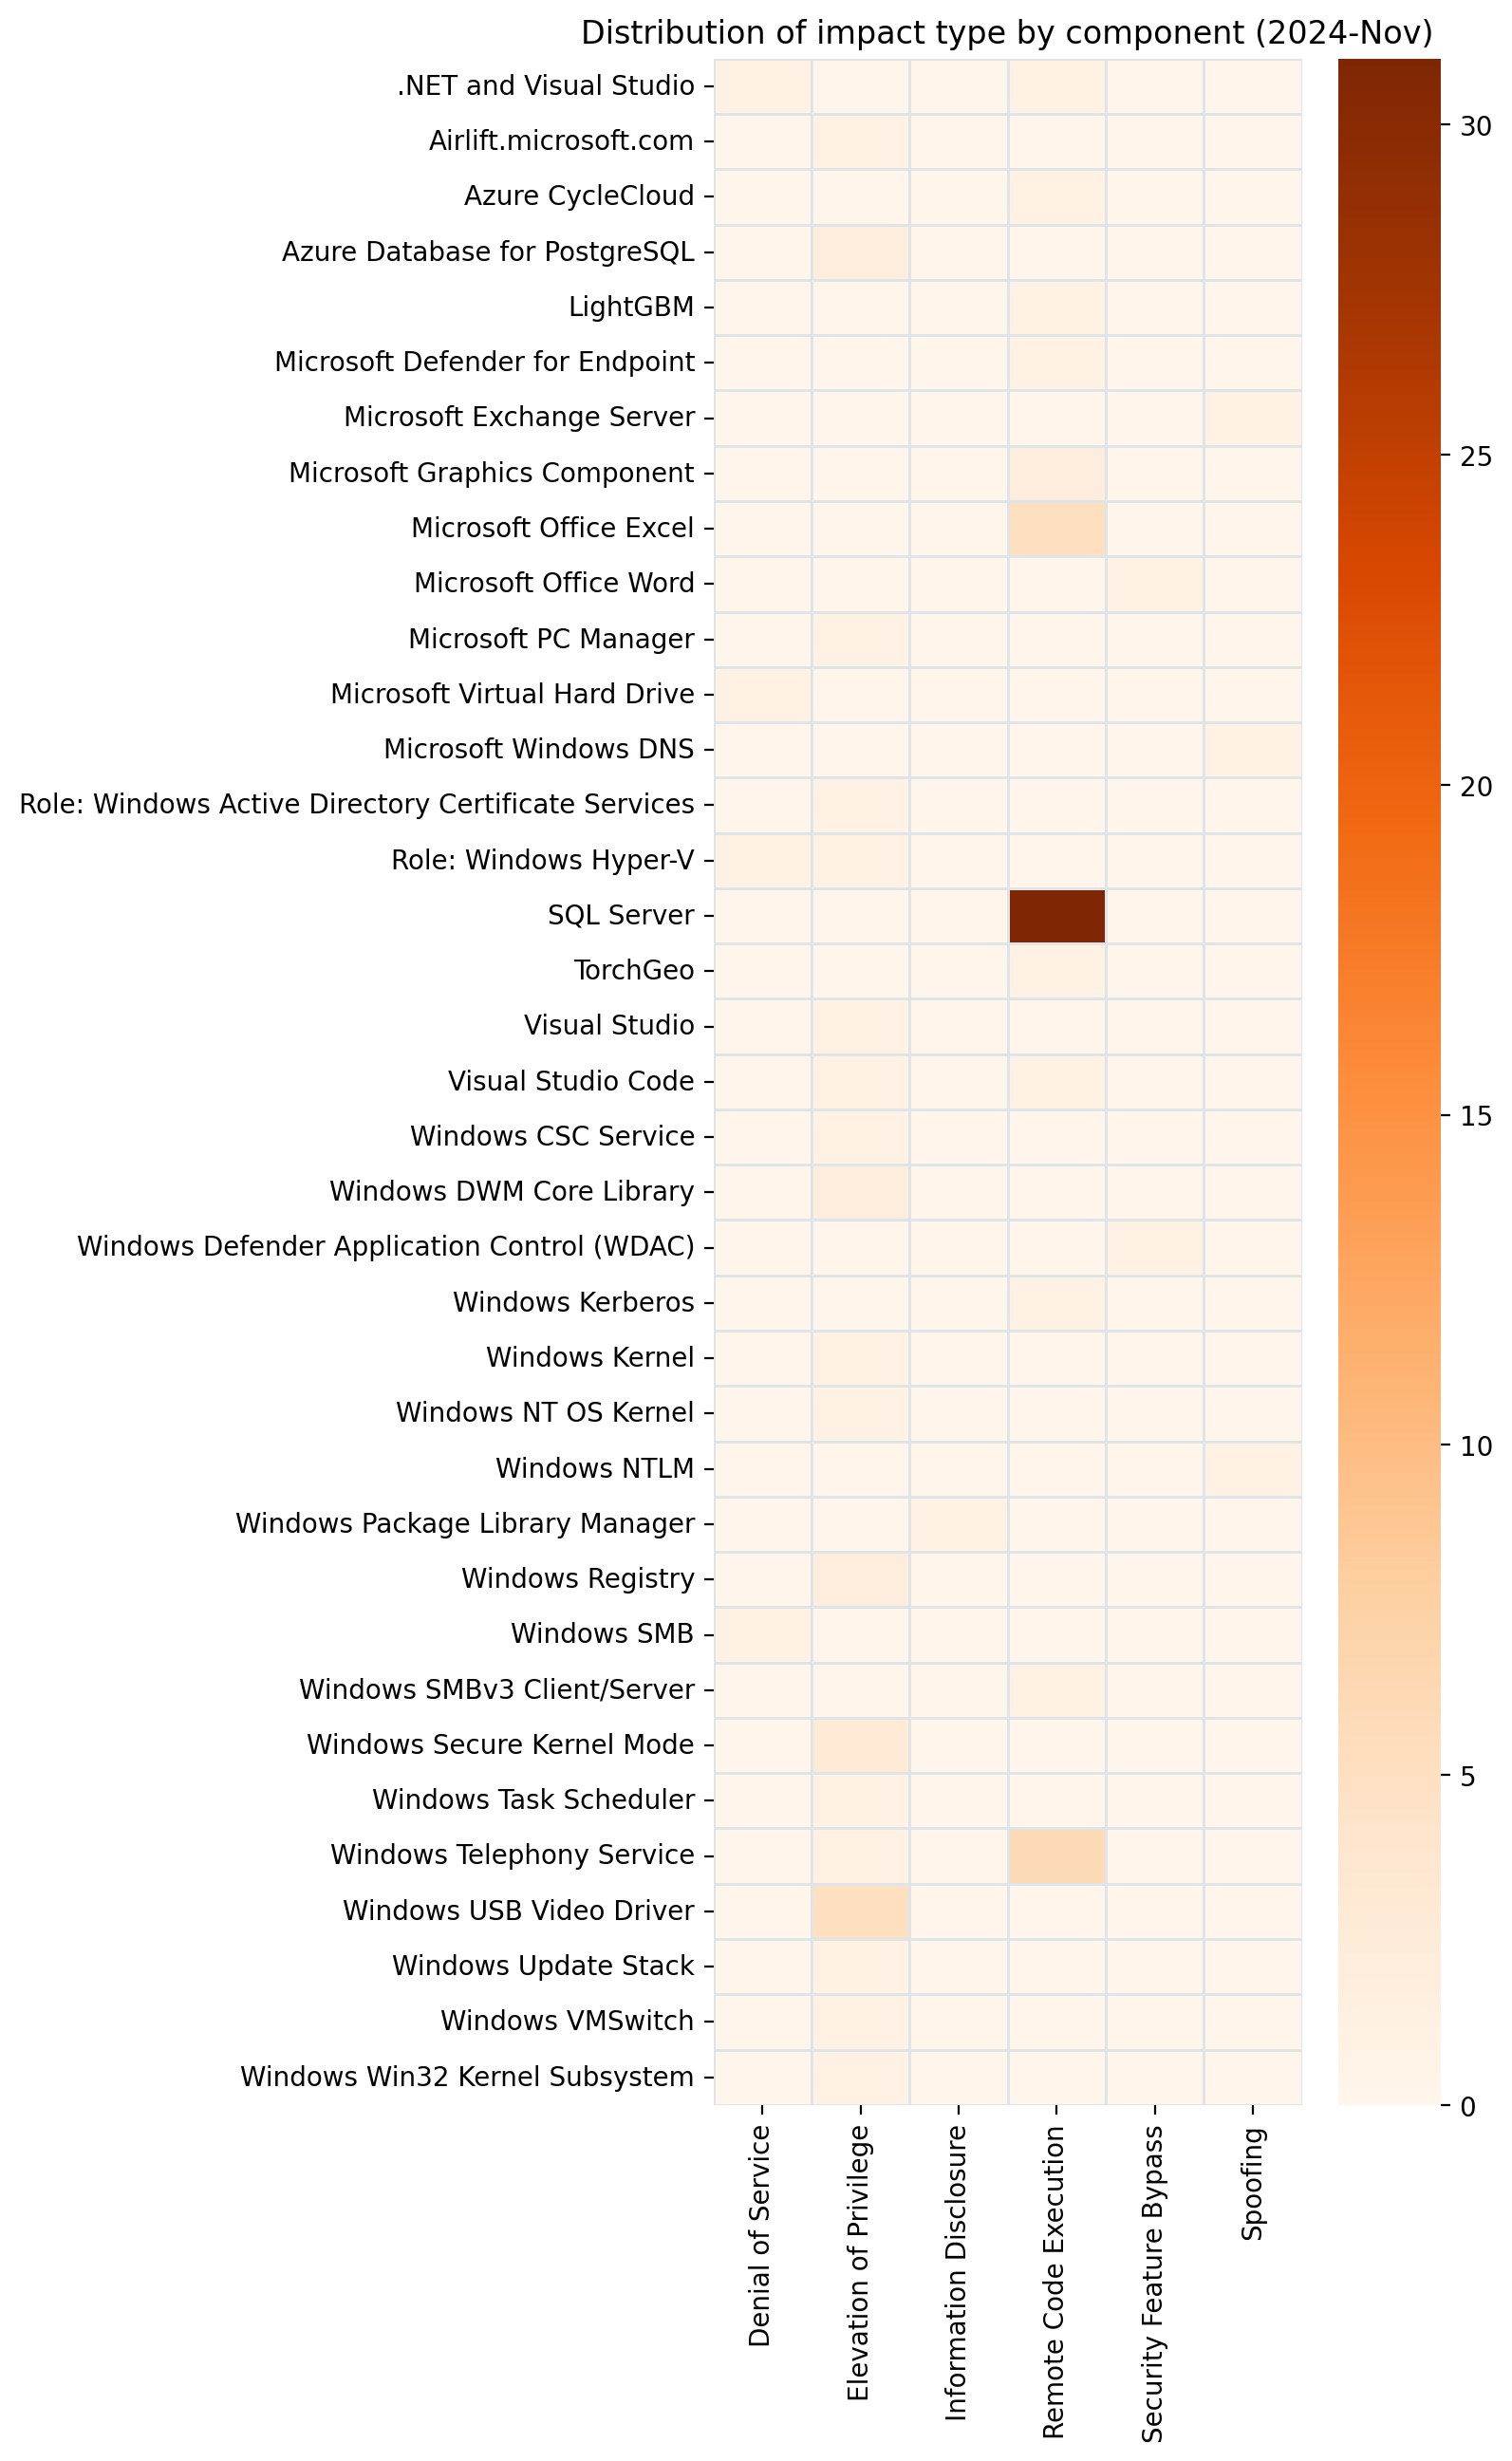
SQL server dominating the heatmap, but it’s mostly a group of closely-related client vulns.
On Wednesday, October 23, 2024, security company Fortinet published an advisory on CVE-2024-47575, a critical zero-day vulnerability affecting their FortiManager network management solution. The vulnerability arises from a missing authentication for a critical function [CWE-306] in the FortiManager fgfmd daemon that allows a remote unauthenticated attacker to execute arbitrary code or commands via specially crafted requests. The vulnerability carries a CVSS v3 score of 9.8.
Fortinet’s advisory notes that CVE-2024-47575 has been “reported” as exploited in the wild. Rapid7 customers have also reported receiving communications from service providers indicating the vulnerability may have been exploited in their environments. According to the vendor, “The identified actions of this attack in the wild have been to automate via a script the exfiltration of various files from the FortiManager which contained the IPs, credentials and configurations of the managed devices.” Rapid7 strongly recommends reviewing the vendor advisory for indicators of compromise and mitigation strategies.
Background
Since roughly October 13, there have been private industry discussions and a number of public posts on Reddit, Twitter, and Mastodon about a rumored zero-day vulnerability in FortiManager. Public Reddit conversations indicated that Fortinet contacted some of their customers by email circa October 15 to “privately disclose” a FortiManager vulnerability and advise on mitigations. Despite embargoed communications and the publication of several newsarticles, neither a public advisory nor a CVE was issued until October 23.
On the evening of October 22, high-profile cybersecurity researcher Kevin Beaumont published a blog alleging that a state-sponsored adversary has been using this FortiManager zero-day vulnerability in espionage attacks. While Fortinet’s advisory doesn’t include any information about specific adversaries exploiting the vulnerability, Fortinet devices have long been popular targets for state-sponsored threat actors.
Mitigation guidance
Per Fortinet’s advisory, the following versions of FortiManager are vulnerable to CVE-2024-47575 and have mitigation guidance available:
FortiManager 7.6.0
FortiManager 7.4.0 through 7.4.4
FortiManager 7.2.0 through 7.2.7
FortiManager 7.0.0 through 7.0.12
FortiManager 6.4.0 through 6.4.14
FortiManager 6.2.0 through 6.2.12
FortiManager Cloud 7.4.1 through 7.4.4
FortiManager Cloud 7.2 (all versions)
FortiManager Cloud 7.0 (all versions)
FortiManager Cloud 6.4 (all versions)
The advisory indicates FortiManager Cloud 7.6 is not affected.
FortiManager customers should update to a supported, fixed version on an emergency basis, without waiting for a regular patch cycle to occur. See the vendor advisory for the latest list of fixed versions. A workaround is also available for some versions.
Fortinet’s advisory also includes a list of indicators of compromise (IOCs) that FortiManager customers should look for in their environments.
Rapid7 customers
InsightVM and Nexpose customers will be able to assess their exposure to CVE-2024-47575 with an authenticated check expected to be available in the Wednesday, October 23 content release.
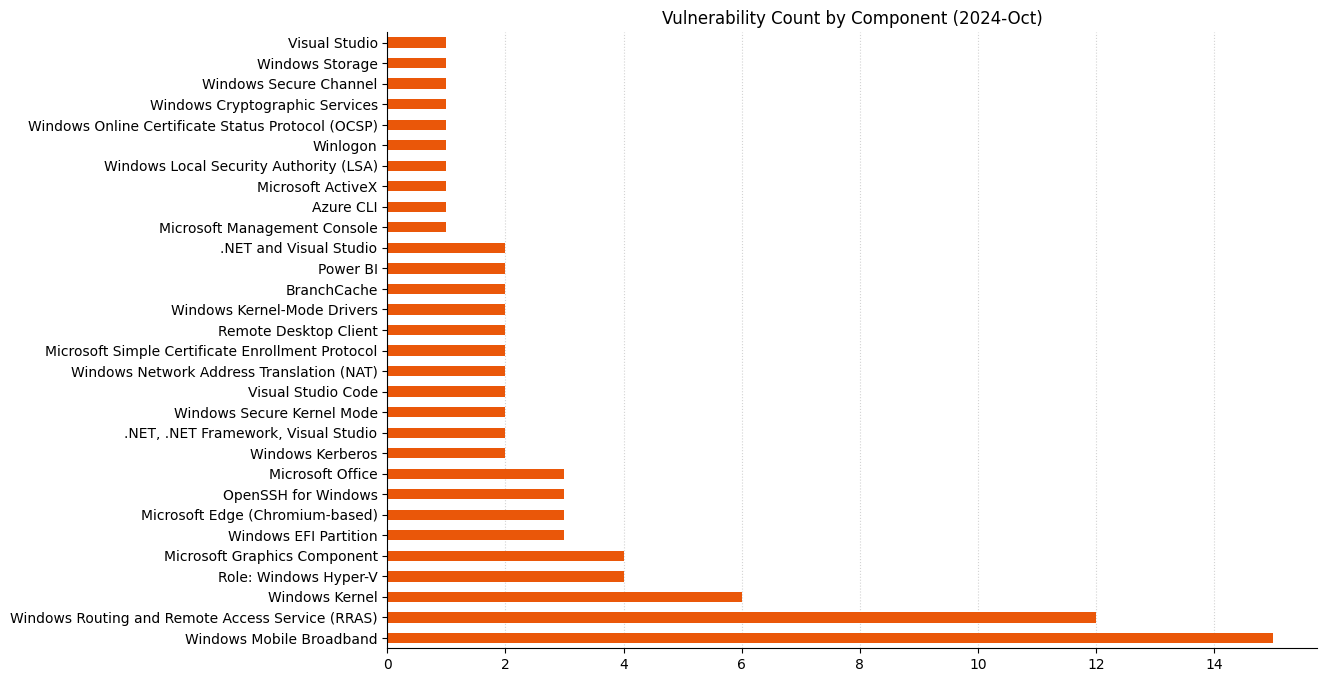
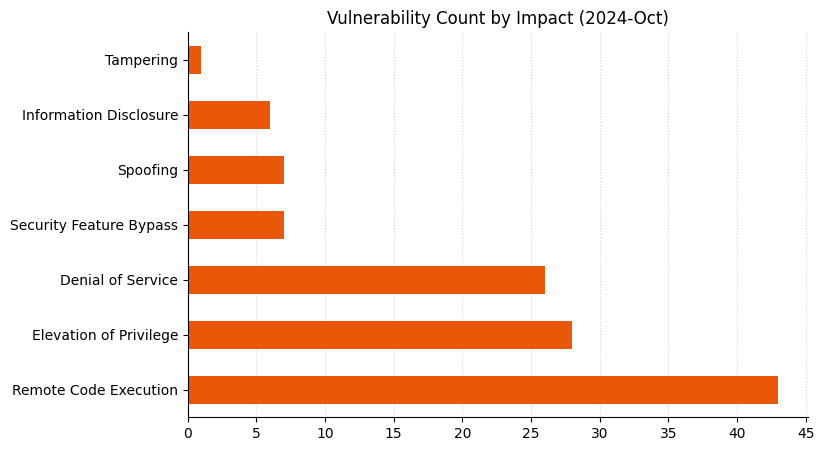
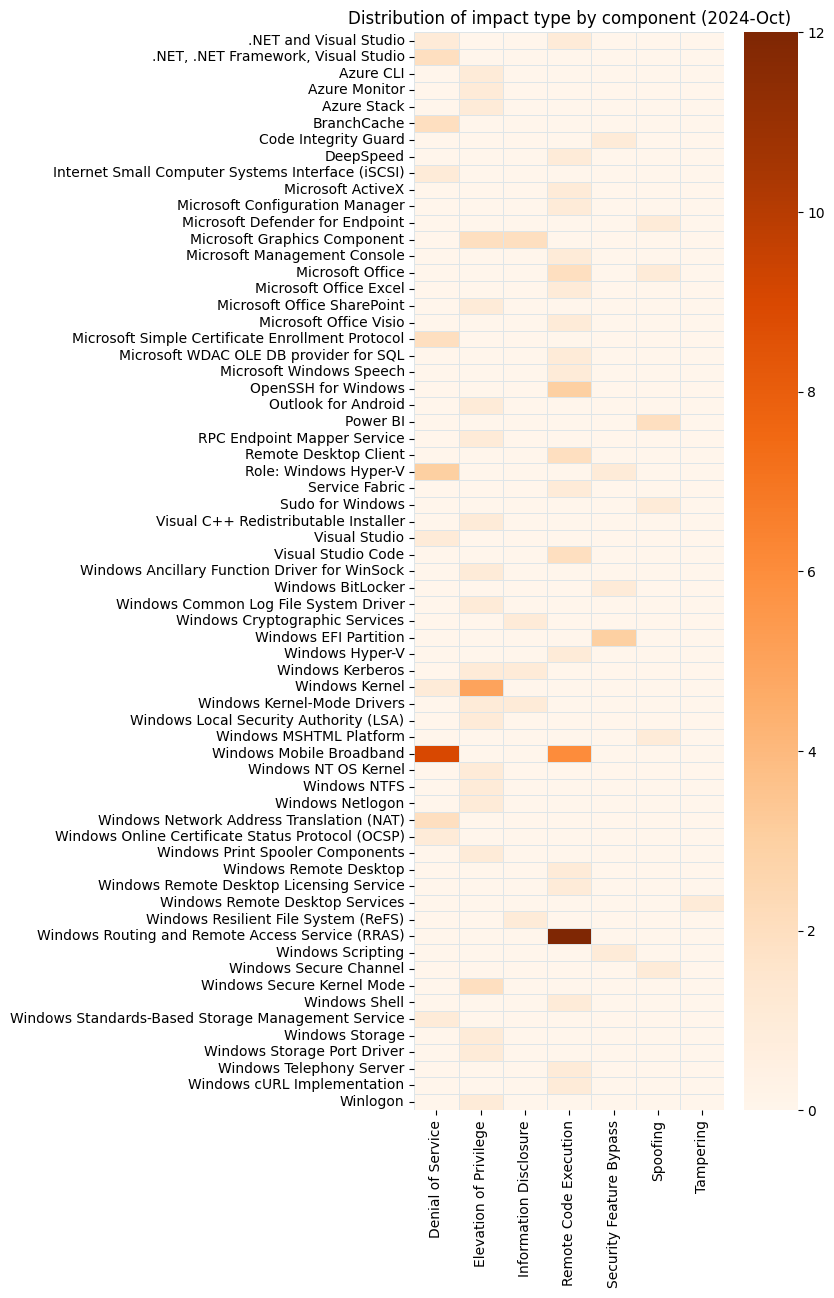
Microsoft is addressing 118 vulnerabilities this October 2024 Patch Tuesday. Microsoft has evidence of in-the-wild exploitation and/or public disclosure for five of the vulnerabilities published today, although it does not rate any of these as critical (yet). Of those five, Microsoft lists two as exploited in the wild, and both of these are now listed on CISA KEV. Microsoft is also patching three further critical remote code execution (RCE) vulnerabilities today. Three browser vulnerabilities have already been published separately this month, and are not included in the total.
Somewhat unusually, we’ll take a look at two of the three critical RCEs published today — CVE-2024-43468 and CVE-2024-43582 — before moving on to the arguably somewhat-less- threatening zero-day vulnerabilities patched today.
Microsoft Configuration Manager: pre-auth RCE
Microsoft Configuration Manager receives a patch for the only vulnerability published by Microsoft today with a CVSS base score of 9.8. Although Microsoft doesn’t tag it as either publicly disclosed or exploited-in-the-wild, the advisory for CVE-2024-43468 appears to describe a no-interaction, low complexity, unauthenticated network RCE against Microsoft Configuration Manager. Exploitation is achieved by sending specially-crafted malicious requests, and leads to code execution in the context of the Configuration Manager server or its underlying database. The relevant update is installed within the Configuration Manager console, and requires specific administrator actions that Microsoft describes in detail in a generic series of articles. Further information and several specific required steps are described in KB29166583.
Confusingly, this KB29166583 was first published over a month ago on 2024-09-04, and was then subsequently unpublished and republished on 2024-09-18, all without any mention of CVE-2024-43468, which was published only today and which KB29166583 apparently remediates. Defenders should read the available documentation carefully, and then probably read it again for good measure.
RPD RPC: pre-auth RCE
Any RDP Server critical RCE is worth patching quickly. CVE-2024-43582 is a pre-auth critical RCE in the Remote Desktop Protocol Server. Exploitation requires an attacker to send deliberately-malformed packets to a Windows RPC host, and leads to code execution in the context of the RPC service, although what this means in practice may depend on factors including RPC Interface Restriction configuration on the target asset. One silver lining: attack complexity is high, since the attacker must win a race condition to access memory improperly.
Winlogon: zero-day EoP
Who doesn’t love a good elevation of privilege vulnerability? Weary blue teamers who see the words “publicly disclosed” on a brand-new advisory know the answer. CVE-2024-43583 describes a flaw in Winlogon which gets an attacker all the way to SYSTEM via abuse of a third-party Input Method Editor (IME) during the sign-on process. The supplementary KB5046254 article explains that the 2024-10-08 patches disable non-Microsoft IME during the sign-in process. On that basis, outright removal of third-party IME is a mitigation available to anyone who is not able to apply today’s patches immediately.
Attack surface reduction is always worth considering, and removal of third-party IMEs certainly accomplishes that. Anyone who needs to keep a third-party IME can still do so, but once today’s patches are applied, that third-party IME will be disabled — only in the context of the sign-in process — to prevent exploitation of CVE-2024-43583. Although Microsoft doesn’t quite spell it out, the only reasonable interpretation of the available information is that an asset with no first-party/Microsoft IME installed would remain vulnerable after patching, since otherwise no IME would be available when attempting to sign in. Use of third-party IME is more likely to be a concern in mixed-language or non-English-speaking contexts. The disclosure process around this vulnerability may not have been entirely smooth; back in September, one of the researchers credited with the discovery expressed discontent with MSRC via X-formerly-known-as-Twitter.
Hyper-V: zero-day container escape
CVE-2024-20659 describes a publicly-disclosed security feature bypass in Hyper-V. Microsoft describes exploitation as both less likely and highly complex. An attacker must be both lucky and resourceful, since only UEFI-enabled hypervisors with certain unspecified hardware are vulnerable, and exploitation requires coordination of a number of factors followed by a well-timed reboot. All this after first achieving a foothold on the same network — although in this context, this likely means access to a VM on the target hypervisor, rather than some other location on the same subnet. The prize for successful exploitation is compromise of the hypervisor kernel.
MSHTML: zero-day XSS
CVE-2024-43573 is an exploited-in-the-wild spoofing vulnerability in MSHTML for which Microsoft is also aware of functional public exploit code; the advisory lists CWE-79 as the weakness, which translates to cross-site scripting (XSS). The advisory is sparse on further detail, although Windows Server 2012/2012 R2 admins who typically install Security Only updates should note that Microsoft is encouraging installation of the Monthly Rollups to ensure remediation in this case. The low CVSSv3 base score of 6.5 reflects the requirement for user interaction and the lack of impact to integrity or availability; a reasonable assumption might be that exploitation leads to improper disclosure of sensitive data, but no other direct effect on the target asset.
cURL: zero-day RCE
Microsoft is most famous for its closed source products, but has cautiously softened its stance on open source considerably in the past quarter century or so. Windows has included components of cURL for almost seven years at this point, along with various other open source components; Microsoft does patch these from time to time, although not always as quickly as defenders might like. Today’s patches for CVE-2024-6197, a publicly-disclosed RCE vulnerability in cURL, continue that trend.
The Microsoft advisory for CVE-2024-6197 clarifies that Windows does not ship libcurl, only the curl command line, but that’s still vulnerable and thus in scope for a fix. Exploitation requires that the user connect to a malicious server controlled by the attacker, and code execution is presumably in the context of the user launching the curl CLI tool on the Windows asset. The cURL project advisory for CVE-2024-6197 was originally published on 2024-07-24, and offers further detail from their perspective. Interestingly, the cURL project describes the most likely outcome of exploitation as a crash, and does not specifically mention RCE, although it is careful not to exclude the possibility of unspecified “more serious results,” which could well mean RCE. Microsoft rates this vulnerability as important, which is on track with the CVSS base score of 8.8.
Management Console: zero-day RCE
CVE-2024-43572 rounds out today’s five zero-day vulnerabilities, and describes a low-complexity, no-user-interaction RCE in Microsoft Management Console. Microsoft is aware of both public functional exploit code and in-the-wild exploitation. The vulnerability is exploited when a user downloads and opens a specially-crafted malicious Microsoft Saved Console (MSC) file, so there’s no suggestion here that the Management Console is vulnerable via network attack. Today’s patches prevent untrusted MSC files from being opened, although the advisory does not describe how Windows will know what’s trusted and what isn’t. Microsoft has chosen to map CVE-2024-43572 to CWE-70, which is a very broad category, the use of which is explicitly discouraged by MITRE.
VS Code Arduino extension: cloud critical RCE
A third critical RCE patched today is hopefully less concerning than its siblings. CVE-2024-43488 is in the Visual Studio Code extension for Arduino, and Microsoft notes that the vulnerability documented by this CVE requires no customer action to resolve. A reasonable question is: what does “no action required” really mean here? Within the advisory, Microsoft both claims to have fully mitigated the vulnerability, and also that there is no plan to fix the vulnerability. As confusing as that all sounds, perhaps the most important takeaway here is that Microsoft is now issuing cloud service CVEs in a stated effort to improve transparency. It’s not clear when the vulnerability was first introduced or when it was remediated, but nevertheless the recent expansion into a whole new class of CVEs is a welcome step by Microsoft.
SharePoint: EoP to SYSTEM
A sparse advisory for CVE-2024-43503, which is an elevation of privilege vulnerability which leads to SYSTEM. Advisories for similar vulnerabilities typically describe the specific SharePoint privileges required, but this one does not, so a reasonable assumption might be that the requirement here is simply minimal Site Member privileges.
In today’s threat landscape, where cyber-attacks are increasingly sophisticated and pervasive, organizations face the daunting challenge of securing a constantly expanding attack surface. Traditional vulnerability management (VM) programs, while necessary, are no longer sufficient on their own. They often struggle to keep pace with the dynamic nature of threats and the complexity of modern IT environments.
This is where continuous threat exposure management (CTEM) comes into play – an approach that shifts the focus from merely identifying vulnerabilities to understanding and mitigating exposures across the entire attack surface.
Implementing a continuous threat and exposure management process
CTEM is a term originally coined by Gartner, who defined it as, “a five-stage approach that continuously exposes an organization’s networks, systems, and assets to simulated attacks to identify vulnerabilities and weaknesses.”
The five stages of CTEM as defined by Gartner are:
Scoping: This involves understanding the full threat landscape by incorporating tools like external attack surface management (EASM) and network scanning. However, it emphasizes the need to think in terms of business context, focusing on crown jewels, critical applications, and understanding what matters most to the organization.
Discovery: This stage focuses on discovering assets and profiling the associated risks. It requires visibility into both cloud and on-premises environments and extends beyond identifying vulnerabilities to include coverage gaps, misconfigurations, and other security risks.
Prioritization: Since not all risks can be addressed simultaneously, this phase involves prioritizing issues based on a combination of factors like severity, exploitability, and potential business impact, to determine what should be tackled first.
Validation: This stage emphasizes investing in tools that help validate security controls and map potential attack paths. It includes the use of breach and attack simulation (BAS) tools, continuous assessment services, controls monitoring, and attack path mapping to test the effectiveness of existing defenses.
Mobilization: The final stage is about taking action. It includes both automation of responses and fostering cross-organizational alignment to ensure that remediation efforts are executed effectively and in sync with business priorities.
This framework helps organizations continuously manage and reduce their exposure to threats in a way that is strategic and aligned to the business.
The role of exposure assessment platforms (EAPs) in CTEM
Exposure assessment platforms (EAPs) are essential to a successful CTEM program. They continuously identify and prioritize exposures, such as vulnerabilities and misconfigurations, across a broad range of asset classes. By consolidating and contextualizing data from various sources, EAPs provide a more comprehensive view of an organization’s risk landscape. This enables security teams to prioritize remediation efforts based on factors such as asset criticality, business impact, and the likelihood of exploitation.
Gartner’s insights into EAPs underscore their importance in modern cybersecurity strategies. By delivering a centralized view of high-risk exposures, EAPs empower organizations to take decisive actions to prevent breaches. They also enhance operational efficiency by offering a unified dashboard that tracks the lifecycle of vulnerabilities and other exposures.
How Rapid7 Exposure Command supports modern vulnerability management programs
Exposure Command is designed to bridge the security-visibility gap many organizations face. By integrating the capabilities of an EAP into a comprehensive security platform, Exposure Command enables organizations to modernize their VM programs and align them with the principles of CTEM.
Exposure Command can help organizations achieve this transformation in a few ways:
Consolidated view of exposures from the inside out and outside in: Exposure Command provides a single, consolidated view of all assets and identified exposures from an internal and external perspective, including vulnerabilities, misconfigurations, and other risk signals. This unified view reduces the overhead associated with managing multiple tools and platforms, enabling security teams to focus on what matters most: mitigating the most critical threats.
Vendor-agnostic approach: As organizations adopt a CTEM approach, they require tools that can evaluate a wide range of exposure telemetry, including security control configurations. Exposure Command excels in this area by leveraging data from existing endpoint and network investments to create a more accurate, situational picture of the organization’s risk landscape. This holistic view is crucial for making informed decisions about where to focus remediation efforts.
Contextualized risk prioritization: Traditional VM programs often rely on CVSS scores to prioritize vulnerabilities, which can lead to misaligned efforts. Exposure Command, however, incorporates threat intelligence, asset criticality, and business impact into its risk-prioritization algorithms. This results in a more accurate and actionable understanding of which exposures pose the greatest risk to the organization.
Identify exploitability and potential for lateral movement: Exposure Command provides the contextual asset enrichment that enables effective threat detection, investigation, and response. The platform showcases how an attacker might exploit vulnerabilities and provides guidance on how to prevent such incidents.
Automated response workflows and deep ecosystem integration: One of the key benefits of Exposure Command is its ability to automate and streamline workflows. By integrating with existing security tools and platforms, Exposure Command can automatically ingest and analyze exposure data, reducing the manual effort required to maintain a VM program. This automation not only improves efficiency but also ensures security teams have access to the most up-to-date information. More and more we’re running into non-patchable systems too, and this deep integration and ability to provide bi-directional workflows enables more effective mobilization across teams, giving actionable feedback to those around the organization who have the ability to execute the necessary remediation actions.
While the benefits of Exposure Command are clear, it’s important to recognize that its effectiveness is tied to the maturity of the organization’s CTEM processes. If these processes are broken or immature, the value of Exposure Command may be limited. However, by adopting an outcome-driven approach that scopes the most critical aspects of the business and correlates asset context with dynamic risk ratings, organizations can maximize the benefits of Exposure Command.
Furthermore, the platform’s ability to integrate with a wide range of tools ensures it can enhance existing security programs, rather than requiring a complete overhaul. This makes it an ideal solution for organizations looking to modernize their VM programs and adopt a more proactive approach to threat management. As you look to strengthen your organization’s cybersecurity posture, consider how Rapid7 Exposure Command can help you bridge the security visibility gap and take a more proactive approach to managing your threat landscape.
On Thursday, September 26, 2024, a security researcher publicly disclosed several vulnerabilities affecting different components of OpenPrinting’s CUPS (Common Unix Printing System). CUPS is a popular IPP-based open-source printing system primarily (but not only) for Linux and UNIX-like operating systems. According to the researcher, a successful exploit chain allows remote unauthenticated attackers to replace existing printers’ IPP URLs with malicious URLs, resulting in arbitrary command execution when a print job is started from the target device.
The vulnerabilities disclosed by the researcher are:
CVE-2024-47176: Affects cups-browsed <= 2.0.1. The service binds on UDP *:631, trusting any packet from any source to trigger a Get-Printer-Attributes IPP request to an attacker-controlled URL.
CVE-2024-47076: Affects libcupsfilters <= 2.1b1. cfGetPrinterAttributes5 does not validate or sanitize the IPP attributes returned from an IPP server, providing attacker-controlled data to the rest of the CUPS system.
CVE-2024-47175: Affects libppd <= 2.1b1. The ppdCreatePPDFromIPP2 API does not validate or sanitize the IPP attributes when writing them to a temporary PPD file, allowing the injection of attacker-controlled data in the resulting PPD.
CVE-2024-47177: Affects cups-filters <= 2.0.1. The foomatic-rip filter allows arbitrary command execution via the FoomaticRIPCommandLine PPD parameter.
According to the researcher’s disclosure blog, affected systems are exploitable from the public internet, or across network segments, if UDP port 631 is exposed and the vulnerable service is listening. CUPS is enabled by default on most popular Linux distributions, but exploitability may vary across implementations. As of 6 PM ET on Thursday, September 26, Red Hat has an advisory available noting that they consider this group of vulnerabilities of Important severity rather than Critical.
Mitigation guidance
We expect patches and remediation guidance to be forthcoming from affected vendors and distributions over the next few days. While the vulnerabilities are not known to be exploited in the wild at time of disclosure, technical details were leaked before the issues were released publicly, which may mean attackers and researchers have had opportunity to develop exploit code. We advise applying patches and/or mitigations as soon as they are available as a precaution, even if exploitability is more limited in some implementations.
Additional mitigation guidance:
Disable and remove the cups-browsed service if it is not necessary
Block or restrict traffic to UDP port 631
Rapid7 customers
InsightVM and Nexpose customers will be able to assess their exposure to these CVEs with authenticated checks that look for affected CUPS packages on UNIX-based systems. These checks are expected to be released in a second content release this evening (ETA 10 PM ET on Thursday, September 26).
We expect to update with additional checks in the coming days as vendors release fixes and more information.
Rapid7 is warning customers about several high-risk vulnerabilities in common enterprise technologies that are attractive potential attack targets for both state-sponsored and financially motivated adversaries. We are advising customers to prioritize remediation for these issues on an expedited basis wherever possible:
CVE-2024-41874: Critical remote code execution vulnerability in Adobe ColdFusion
CVE-2024-38812, CVE-2024-38813: Remote code execution and privilege escalation vulnerabilities (respectively) in Broadcom VMware vCenter Server and Cloud Foundation
On September 10, 2024, Adobe published a critical advisory for CVE-2024-41874, an unauthenticated remote code execution issue that occurs as a result of unsafe Web Distributed Data eXchange (“Wddx”) packet deserialization. Rapid7 MDR has previously observed exploitation that targets Wddx for remote code execution; we have also previously observed exploitation of multiple other ColdFusion CVEs.
Affected products and mitigation: Adobe ColdFusion 2023 (update 9 and earlier) and Adobe ColdFusion 2021 (update 15 and earlier) are vulnerable to CVE-2024-41874. The vulnerability is resolved in versions 10 and 16, respectively. For more information, see the vendor advisory.
Broadcom VMware vCenter Server CVEs
On September 17, 2024, Broadcom published an advisory on CVE-2024-38812, a critical heap overflow vulnerability affecting VMware vCenter Server. Successful exploitation of CVE-2024-38812 allows an attacker with network access to the vulnerable server to execute code remotely on the target system. CVE-2024-38813, a local privilege escalation vulnerability, was also reported by the same researchers, making this a full-chain exploit. We are not aware of exploitation in the wild as of September 19, 2024, but vCenter Server is a high-value attack target for ransomware and extortion groups.
Affected products and mitigation: Broadcom VMware vCenter Server 7.0 and 8.0 are vulnerable to CVE-2024-38812 and CVE-2024-38813. Fixes are available as indicated in the vendor advisory. Broadcom also has an FAQ available.
Ivanti Endpoint Manager CVE-2024-29847
On September 10, 2024, Ivanti published a security advisory on CVE-2024-29847, an unsafe deserialization vulnerability in Ivanti Endpoint Manager (EPM) solution. Successful exploitation allows unauthenticated attackers to execute code remotely on target systems. Vulnerability details and proof-of-concept exploit code are available.
Affected products and mitigation: Ivanti Endpoint Manager (EPM) 2022 SU5 (and earlier) and EPM 2024 are vulnerable to CVE-2024-29847. Customers using EPM 2022 can remediate this and other recent vulnerabilities by updating to 2022 SU 6. Per Ivanti’s security advisory, EPM 2024 customers can apply an available security patch while waiting for 2024 SU1, which is yet to be released. See Ivanti’s advisory for the latest information.
Rapid7 customers
InsightVM and Nexpose customers can assess their exposure to Adobe ColdFusion CVE-2024-41874 and Broadcom VMware vCenter Server CVE-2024-28812 and CVE-2024-38813 with vulnerability checks released previously. A vulnerability check for Ivanti EPM CVE-2024-29847 is in development and is expected to be available in tomorrow’s (Friday, September 20) content release.
The collective thoughts of the interwebz
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.