Once a month, Microsoft pushes a security update to all Windows users. Tomorrow’s is a new record:
Microsoft’s patch for September is a doozy, with a record number of roughly 972 vulnerabilities fixed and 112 of them meeting the high critical-severity threshold.
It was only two months ago that Microsoft patched a then-record 570 vulnerabilities. Then, last month, Microsoft patched some 620 of them. Google and other companies have also published record numbers of vulnerabilities in recent months. Two weeks ago, OpenAI, Anthropic, Amazon Web Services, Google, Microsoft, and 100 companies and organizations published an open letter warning of a narrowing window for patching vulnerabilities ahead of an expected tsunami of AI-enabled attacks that actively exploit them first. The industry is taking the threat seriously by pumping out unprecedented numbers of patches in their software.
This is the result of AI-powered vulnerability finding, and a good example of AI helping the defenders more than the attackers.
What will be interesting to watch is how the number of vulnerabilities changes over the next few months. My prediction is that it will continue to increase as the AIs get better at finding software vulnerabilities, and then decrease as they run out of vulnerabilities to find. How high the number gets, how fast the trend reverses, and how quickly it declines after that are all unknown.
And Microsoft is right: The window to patch has shrunk to “immediately.” AIs are also good at reverse-engineering exploits from patches, which means that these vulnerabilities will be weaponized as soon as the update is published.
Windows environments provide a variety of approaches for monitoring both on the OS and the application level. The article will cover utilizing Zabbix agent on Windows to collect and discover OS and application level metrics from a variety of Windows-supported sources.
Deploying Zabbix agent on Windows
Zabbix agent can be deployed either by downloading the official MSI packages or by installing the Zabbix agent from binary files. Both Zabbix agent and Zabbix agent 2 are available to install via these methods. Generally speaking, Zabbix agent 2 is a more feature-rich version than the regular Zabbix agent. On the other hand, if you do encounter any compatibility issues with Zabbix agent 2 – the classic Zabbix agent can be used instead.
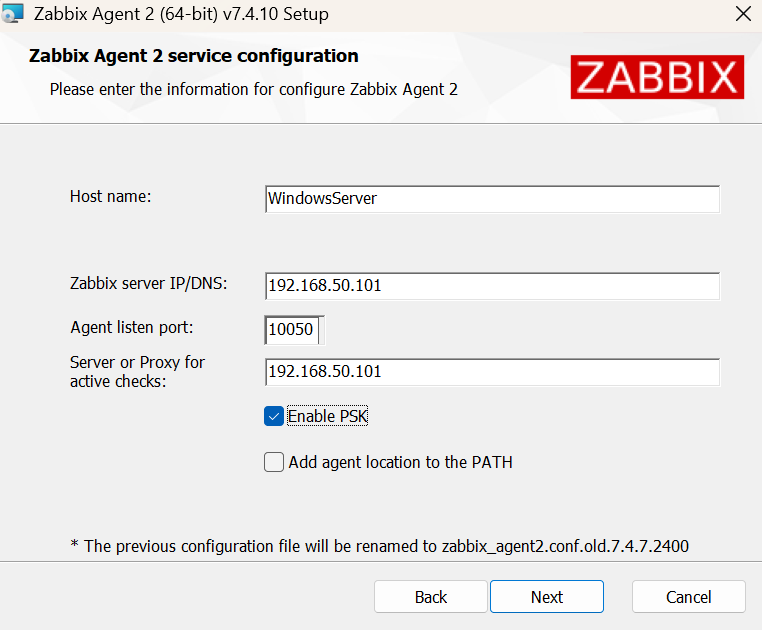
During the MSI install the following Zabbix agent configuration parameters can be defined:
Zabbix server address
Zabbix agent PSK encryption settings
Direction of the connection (Active/Passive checks)
Optional install of Zabbix sender and Zabbix get tools
Configure basic Zabbix agent parameters during the MSI install
Installing Zabbix agent from binary file is also a fast and simple process:
Download the Zabbix agent binary files
Adjust the Zabbix agent configuration file to fit your requirements
Run the agent binary file with the —install command
Use the –config command to point the Zabbix agent at the agent configuration file
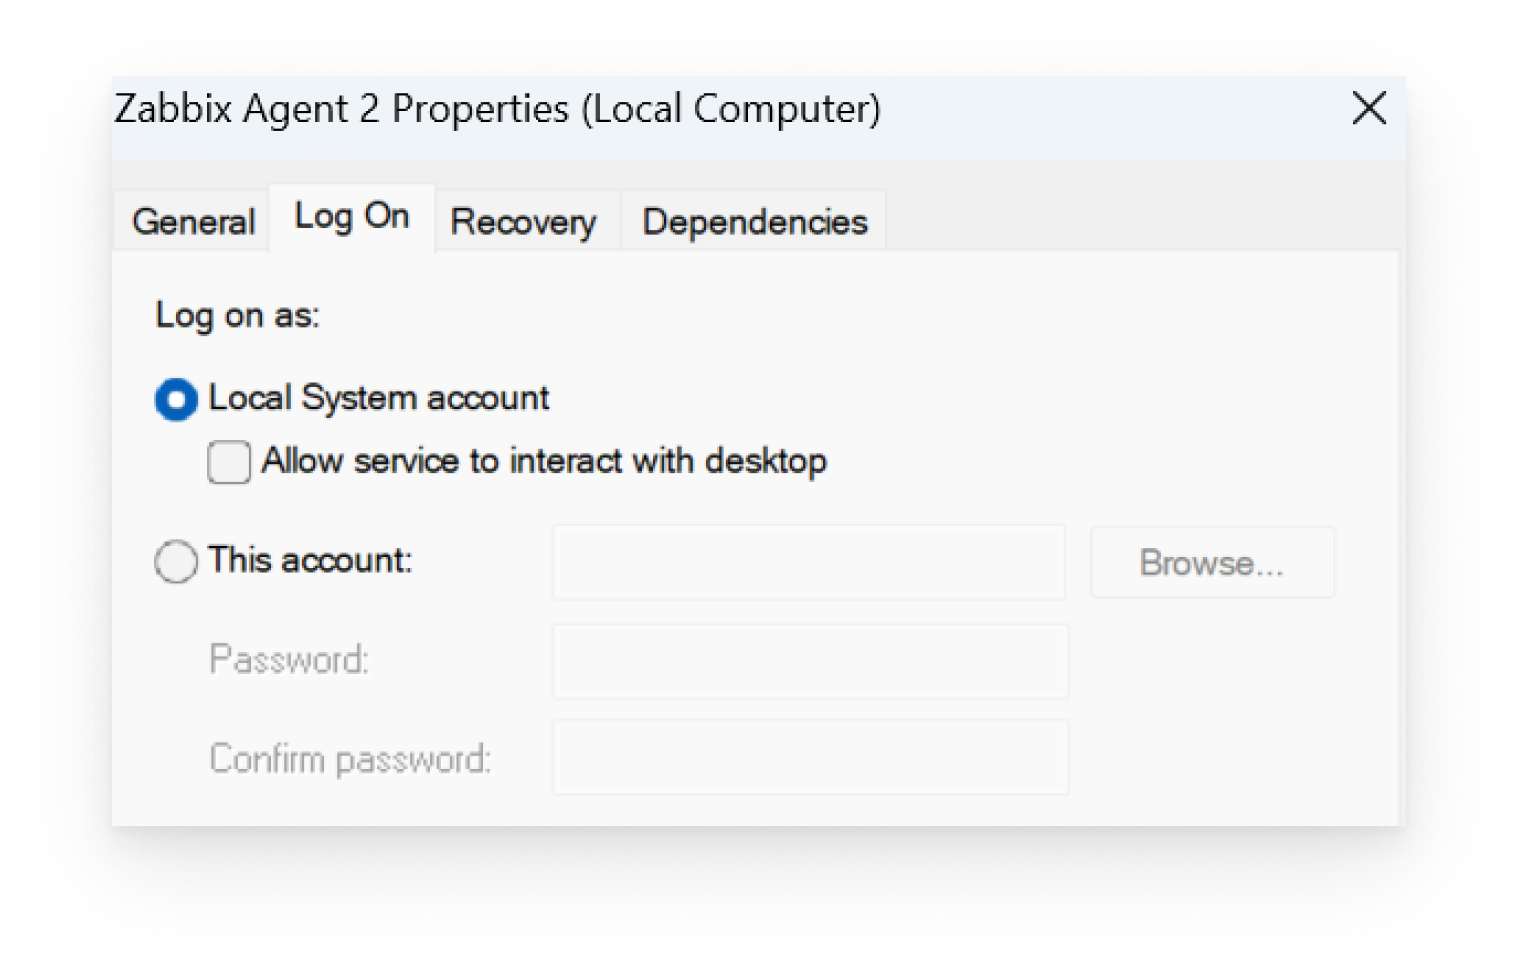
As a result of both approaches, Zabbix agent will be installed and run as a Windows service. By default the agent runs under the Local System account (Having unrestricted access to local system resources) – this can and should be adjusted based on your organizational security policies.
By default Zabbix agent service runs under Local System account
Additional Zabbix agent 2 plugins
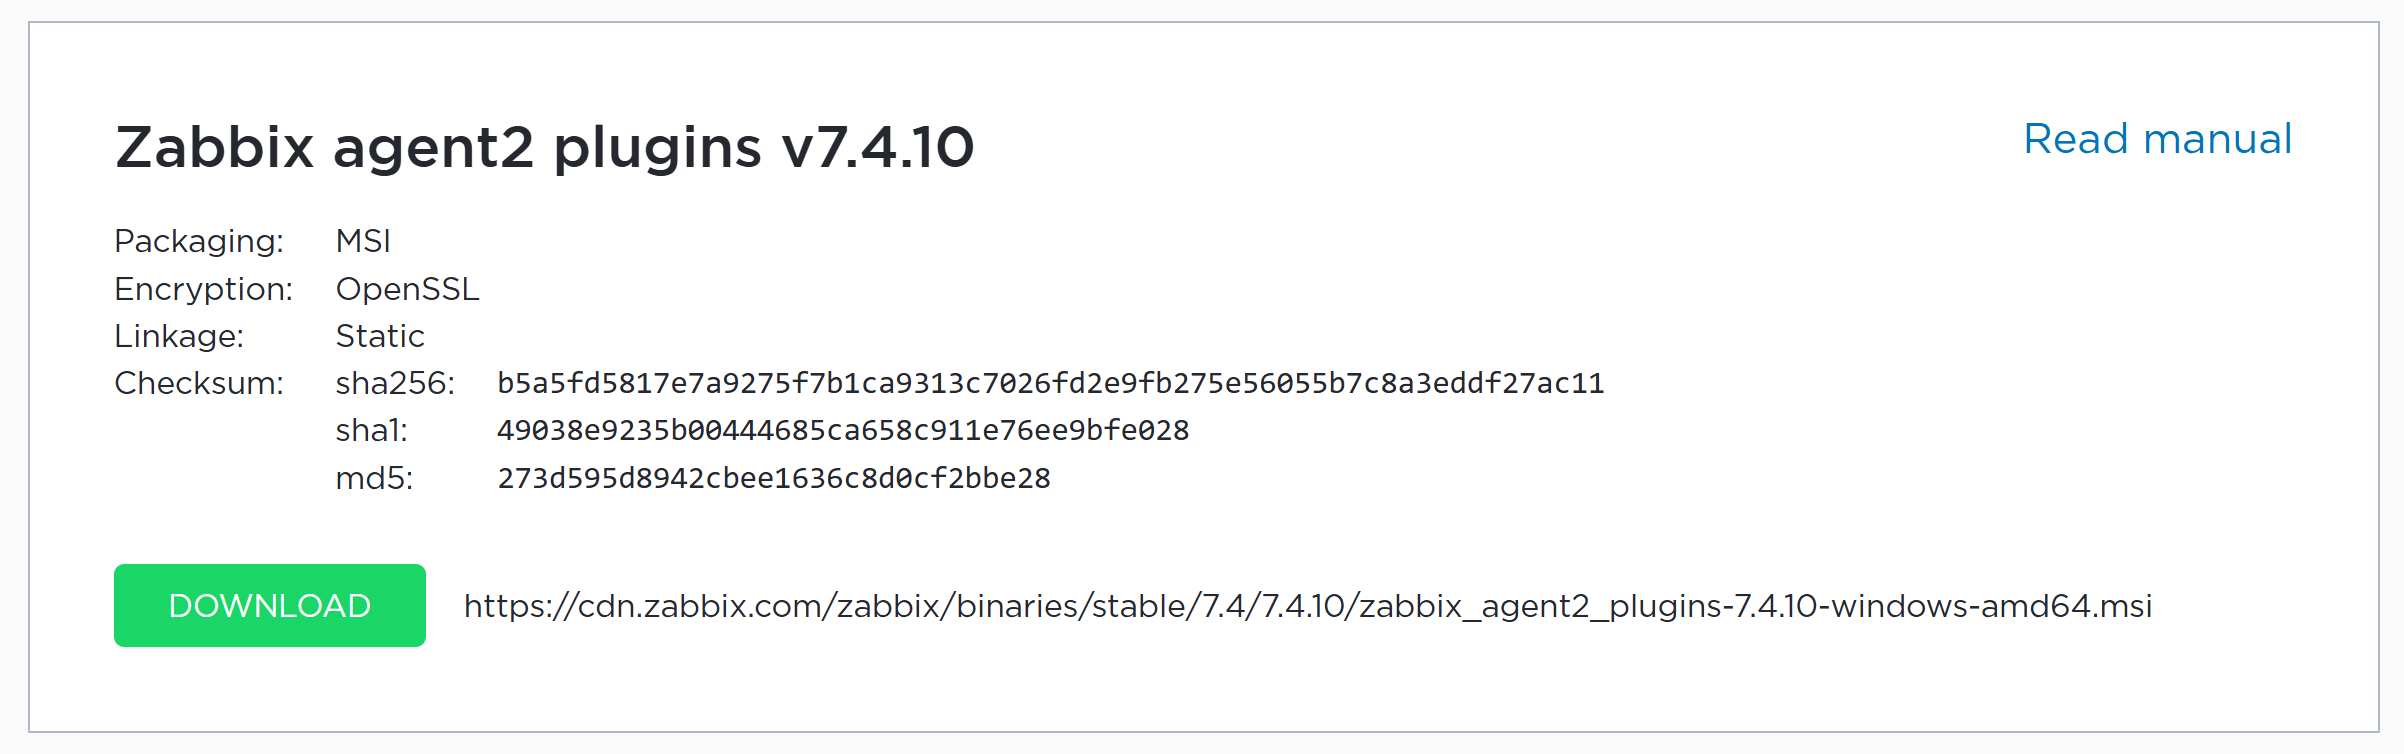
Multiple Zabbix agent 2 plugins are provided in a separate package, which can also be installed via the MSI installer. The following plugins have to be installed via the dedicated Zabbix agent 2 plugins package:
Ember plus
MongoDB
MSSQL
NVIDIA GPU
PostgreSQL
Additional Zabbix agent 2 plugins are available in a separate package
Configuring a Windows host in Zabbix
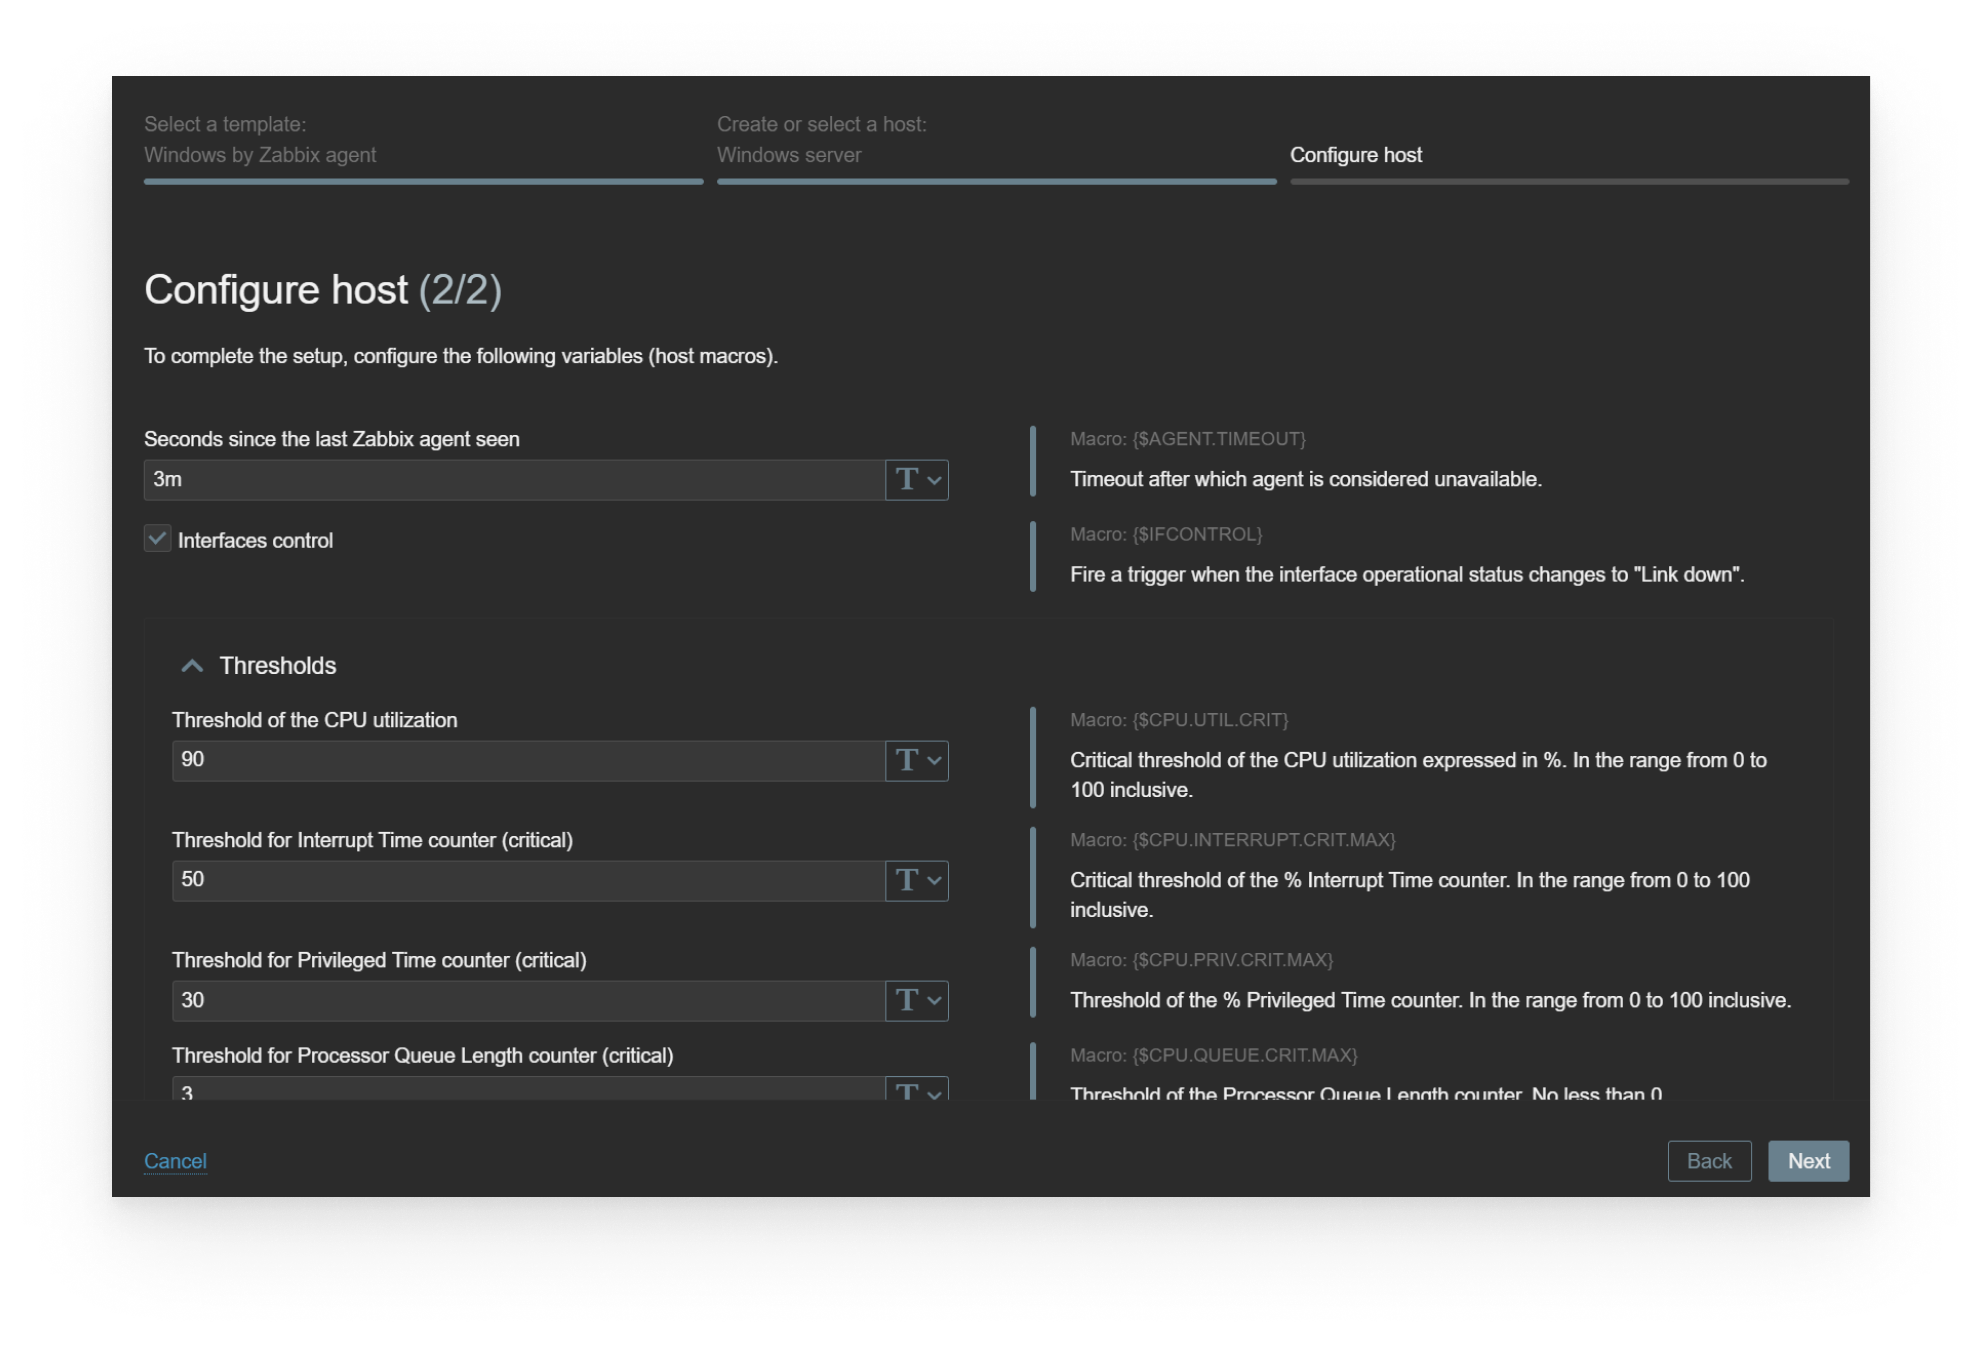
The quickest way to get started once the agent is deployed and configured, is to create a Windows host in Zabbix and use one of the official Zabbix templates on this host. The host can be either created manually or by using the Host Wizard for a more guided experience (Host Wizard is available starting from Zabbix 7.4).
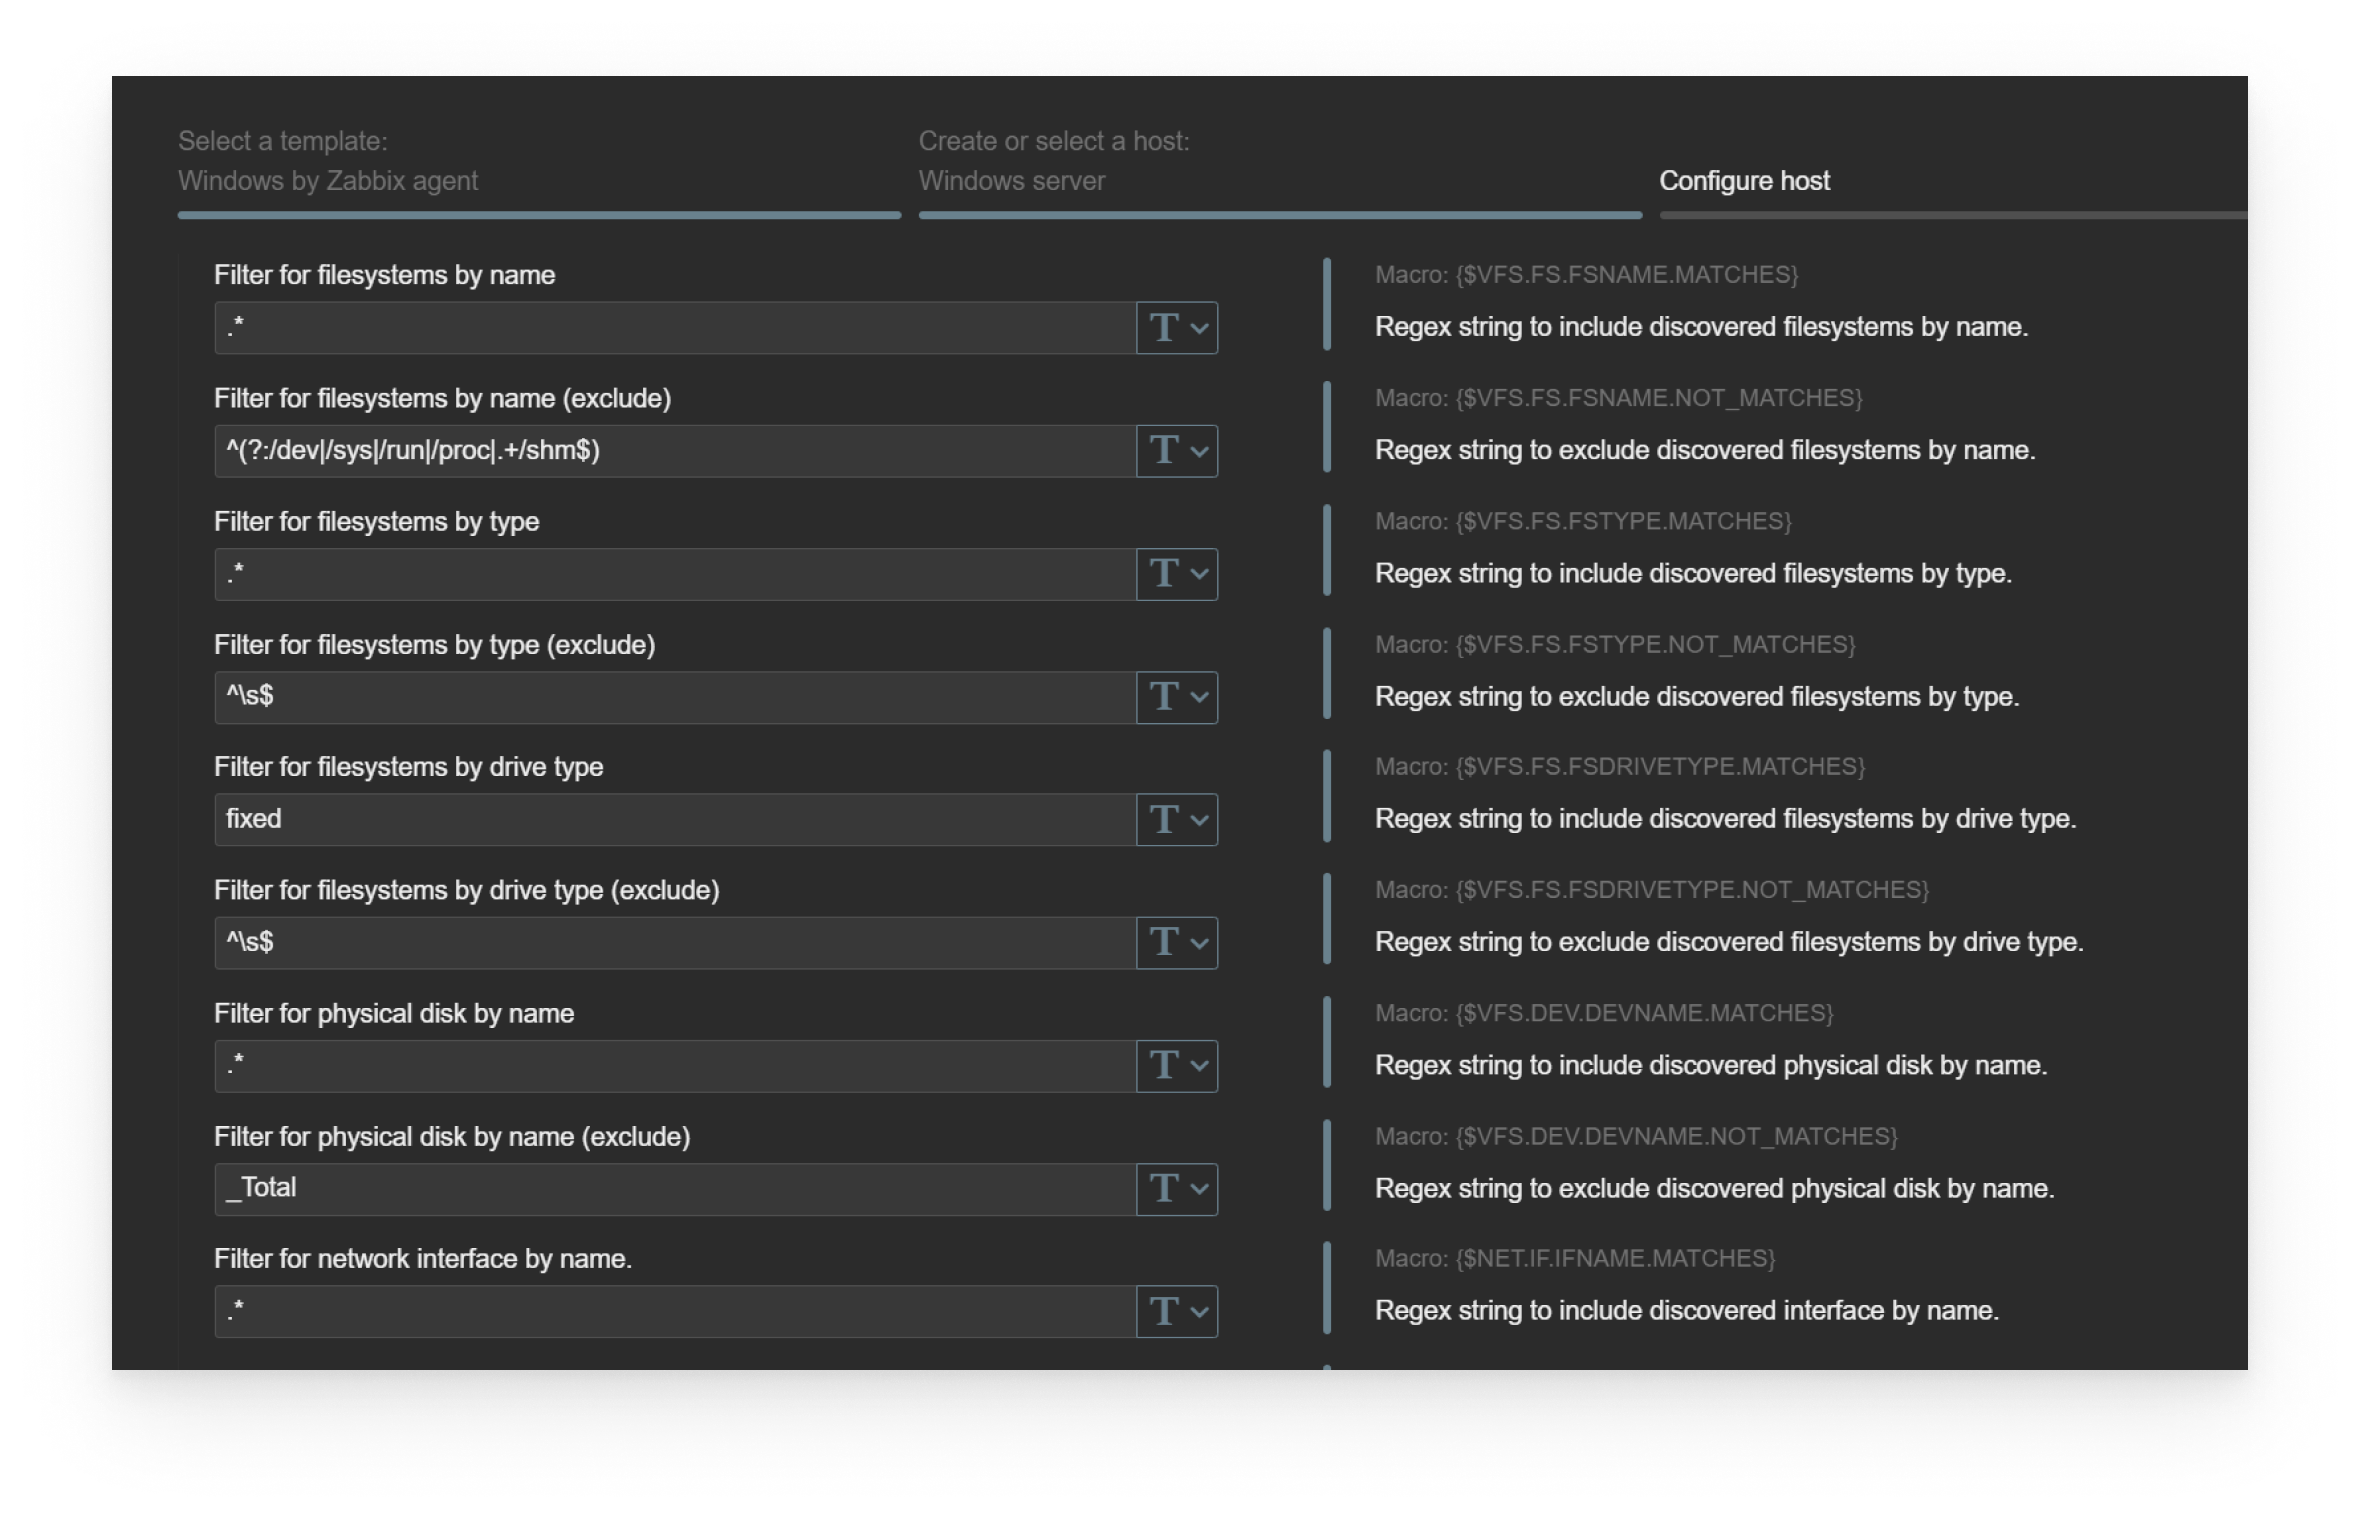
After you have assigned the template, adjust the macros used for trigger thresholds and low-level discovery filters on the host level, so they fit your individual requirements. (Once again – the Host Wizard will guide you through this process during the host creation. Otherwise – open the Macros section in the host configuration and adjust them manually)
A guided host configuration is available by using Zabbix Host Wizard
Official Zabbix templates for Windows environments
Zabbix provides a variety of templates for Windows OS and application monitoring:
Windows by Zabbix agent
MSSQL by Zabbix agent 2
Microsoft SharePoint by HTTP
Microsoft Exchange Server 2016 by Zabbix agent
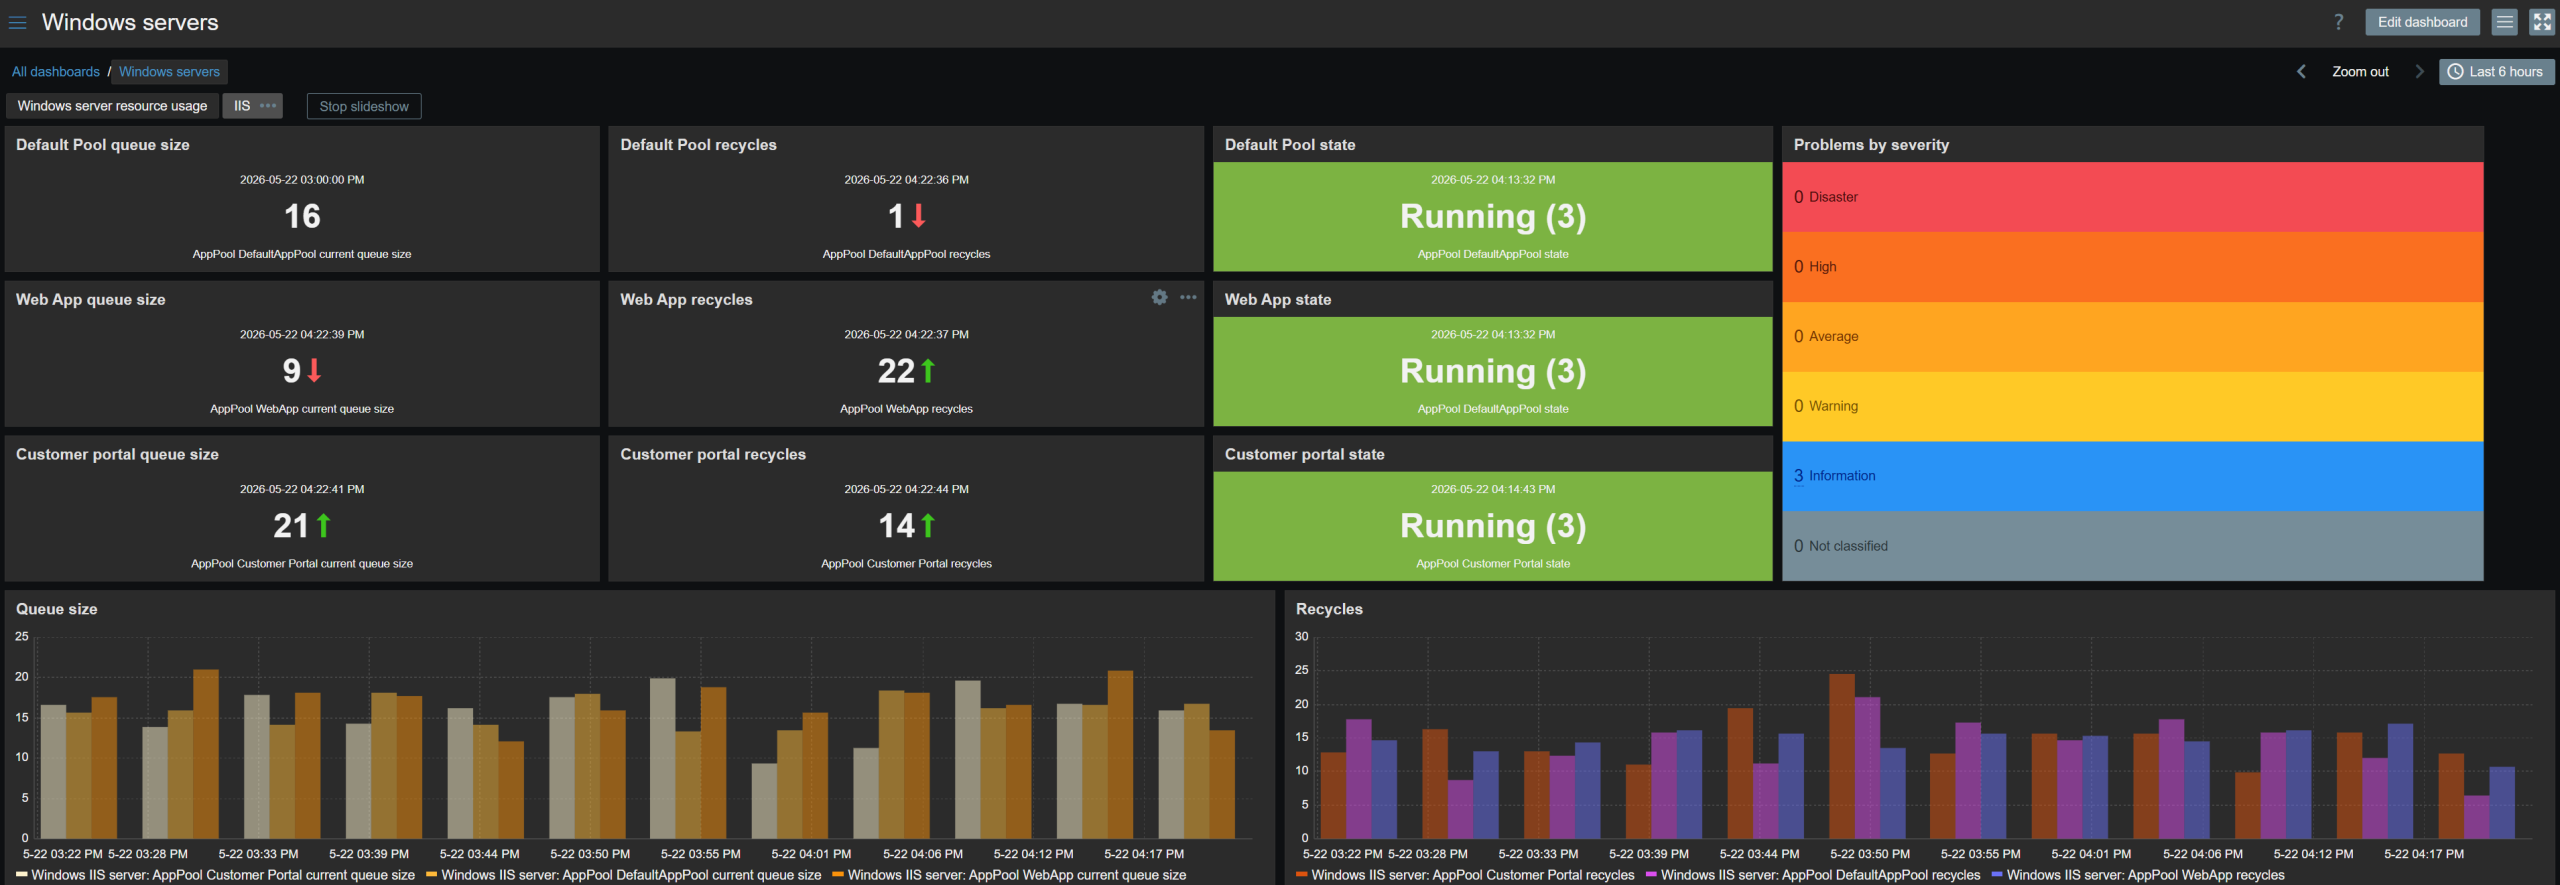
IIS by Zabbix agent
The templates contain static items, triggers, graphs and dashboards as well as a variety of low-level discovery rules to discover resources such as:
Depending on the application, additional configuration might be required on the application side. The required configuration steps are documented in the corresponding integration pages on our website.
Performance counters and WMI queries
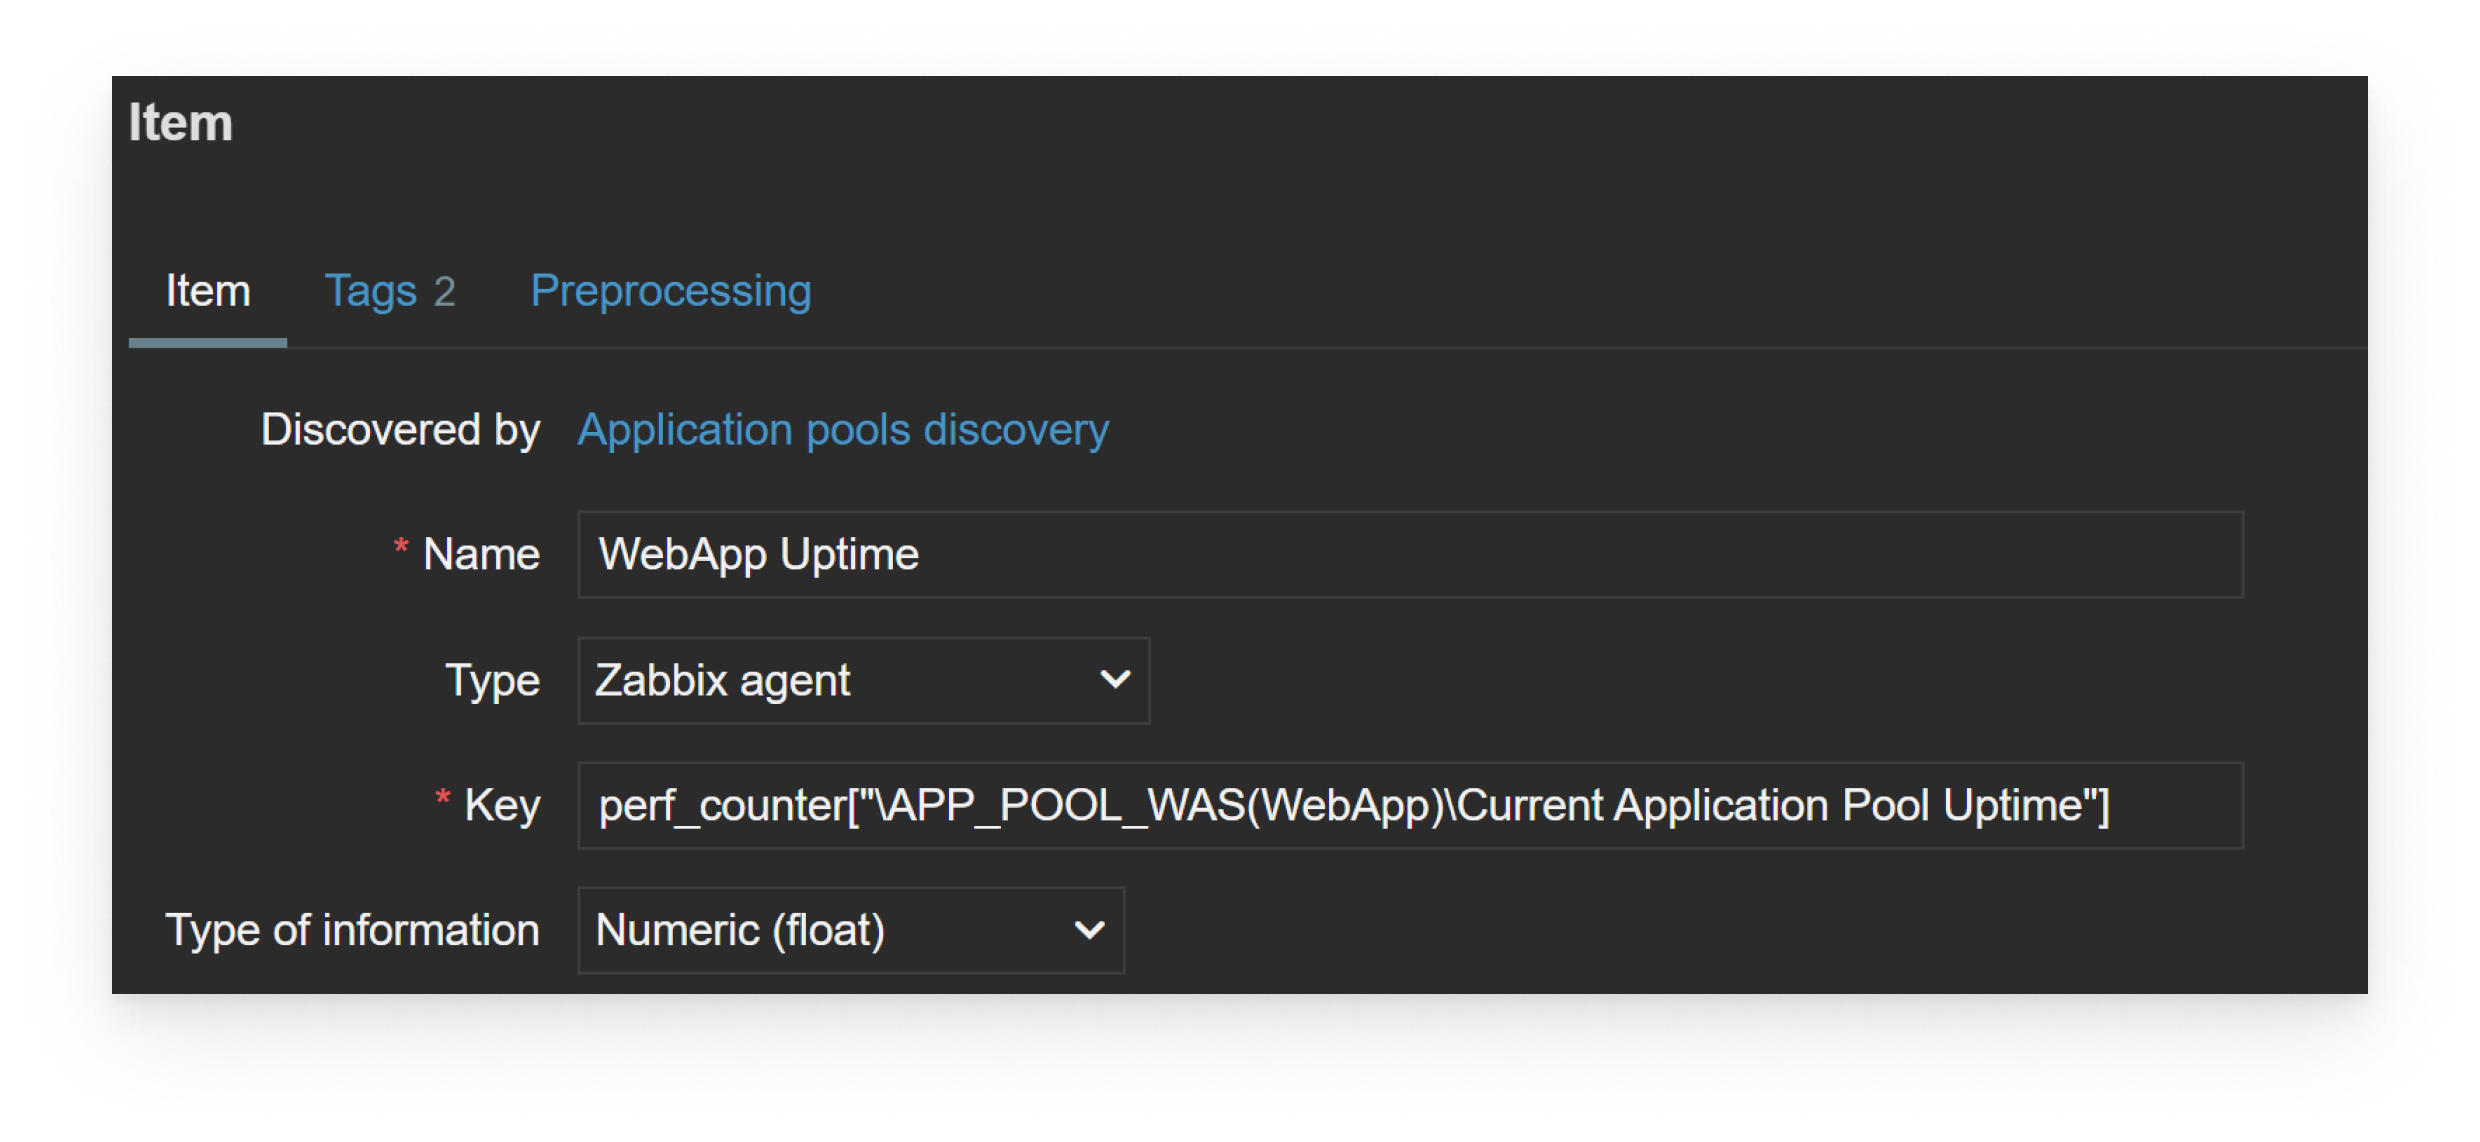
Performance counters are used both in our official templates and are also a common way how existing templates can be extended and templates for other Windows applications can be built.
Performance counter monitoring is done by using a Zabbix agent item key – perf_counter[]
With this approach you can configure your Zabbix agent to collect any supported performance counter value. For example, here’s a performance counter item key for monitoring IIS application pool state:
perf_counter[“\APP_POOL_WAS(Customer Portal)\Current Application Pool State”]
The item key can also use performance counter indexes (numeric performance counter representations).
To ensure that performance counter items remain portable across different Windows hosts with different Windows locales, Zabbix provides English performance counter item key – perf_counter_en[].
Performance counters can be used to extend Zabbix agent native monitoring capabilities
In addition to performance counters, Zabbix agent can also execute WMI (Windows Management Instrumentation) queries.
Two keys can be used to collect WMI data:
get[<namespace>,<query>] – return the first selected object
getall[<namespace>,<query>] – return the whole response in JSON (Can be used for low-level discovery)
For example – return the status of the first physical disk: wmi.get[root\cimv2,select status from Win32_DiskDrive where Name like ‘%PHYSICALDRIVE0%’]
Windows log monitoring
Zabbix agent provides 2 item keys specifically for Windows event log monitoring:
Collect the event log entry matching the item key parameters: eventlog[name,<regexp>,<severity>,<source>,<eventid>,<maxlines>,<mode>]
Collect the number of matching event log entries ofr a time period: count[name,<regexp>,<severity>,<source>,<eventid>,<maxproclines>,<mode>]
The event log entries can be filtered by log name, log contents (via a regular expression), log severity, source, and event ID.
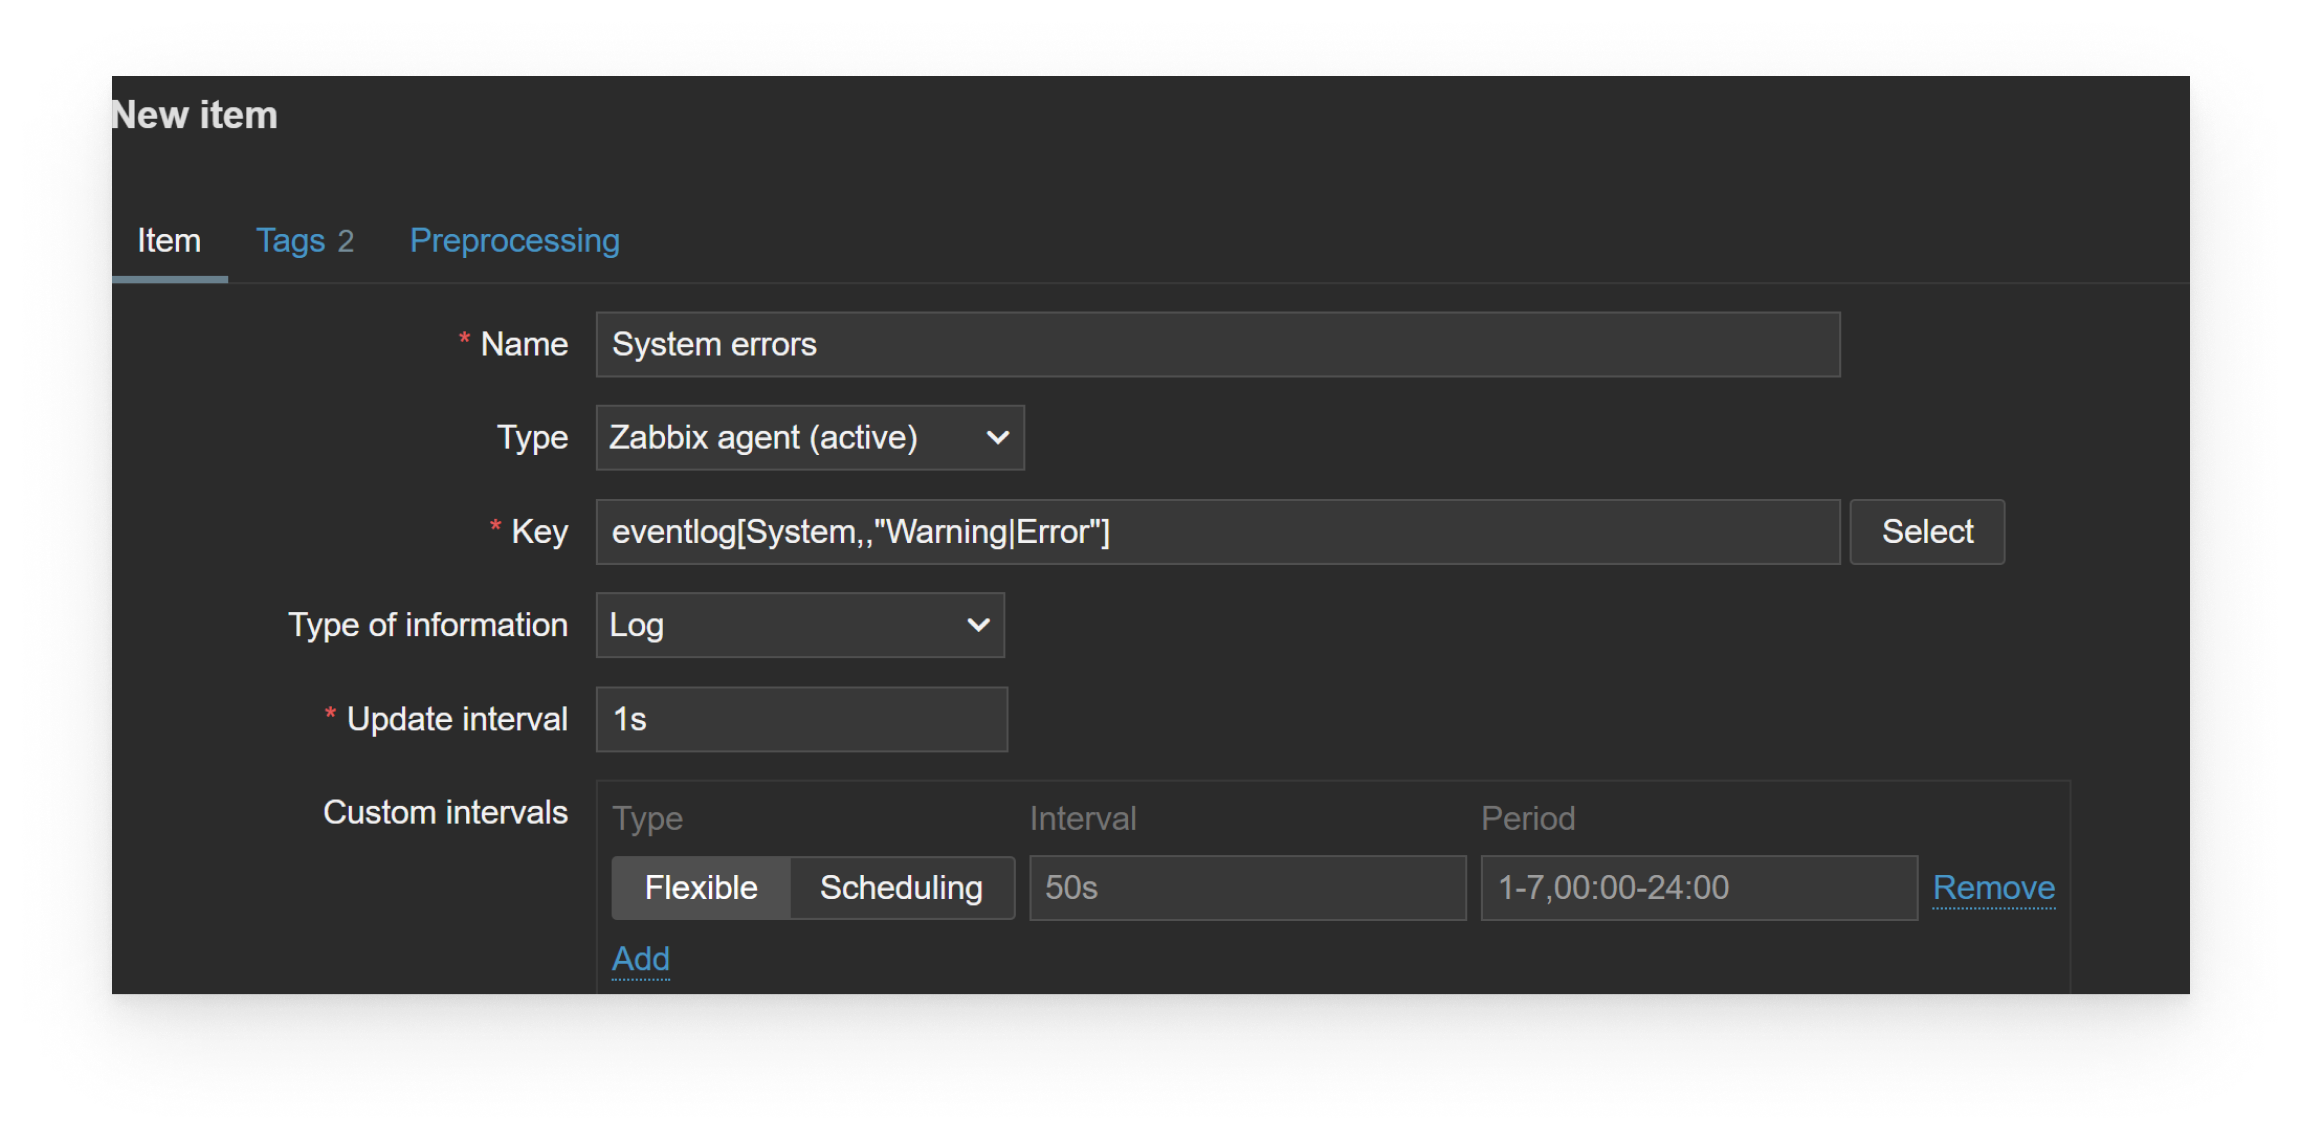
For example, we might want to react only to log entries in the System log with entry severity matching Warning or Error.
eventlog item can filter log entries by various attributes
Here the regular log monitoring guidelines apply – it’s supported only by Zabbix agent active checks with the recommended update interval of 1 second (except for eventlog.count) and have a dedicated Type of information with a unique set of configuration settings.
Extending Zabbix agent on Windows
In addition to custom performance counters and WMI queries, Zabbix agent installations on Windows installations can be extended in standard Zabbix ways:
Defining Zabbix agent User parameters with custom item keys
Using Zabbix agent system.run item to run custom scripts and commands
Since Zabbix agent is language-agnostic, we can utilize Windows-specific PowerShell scripts or commands to collect custom data:
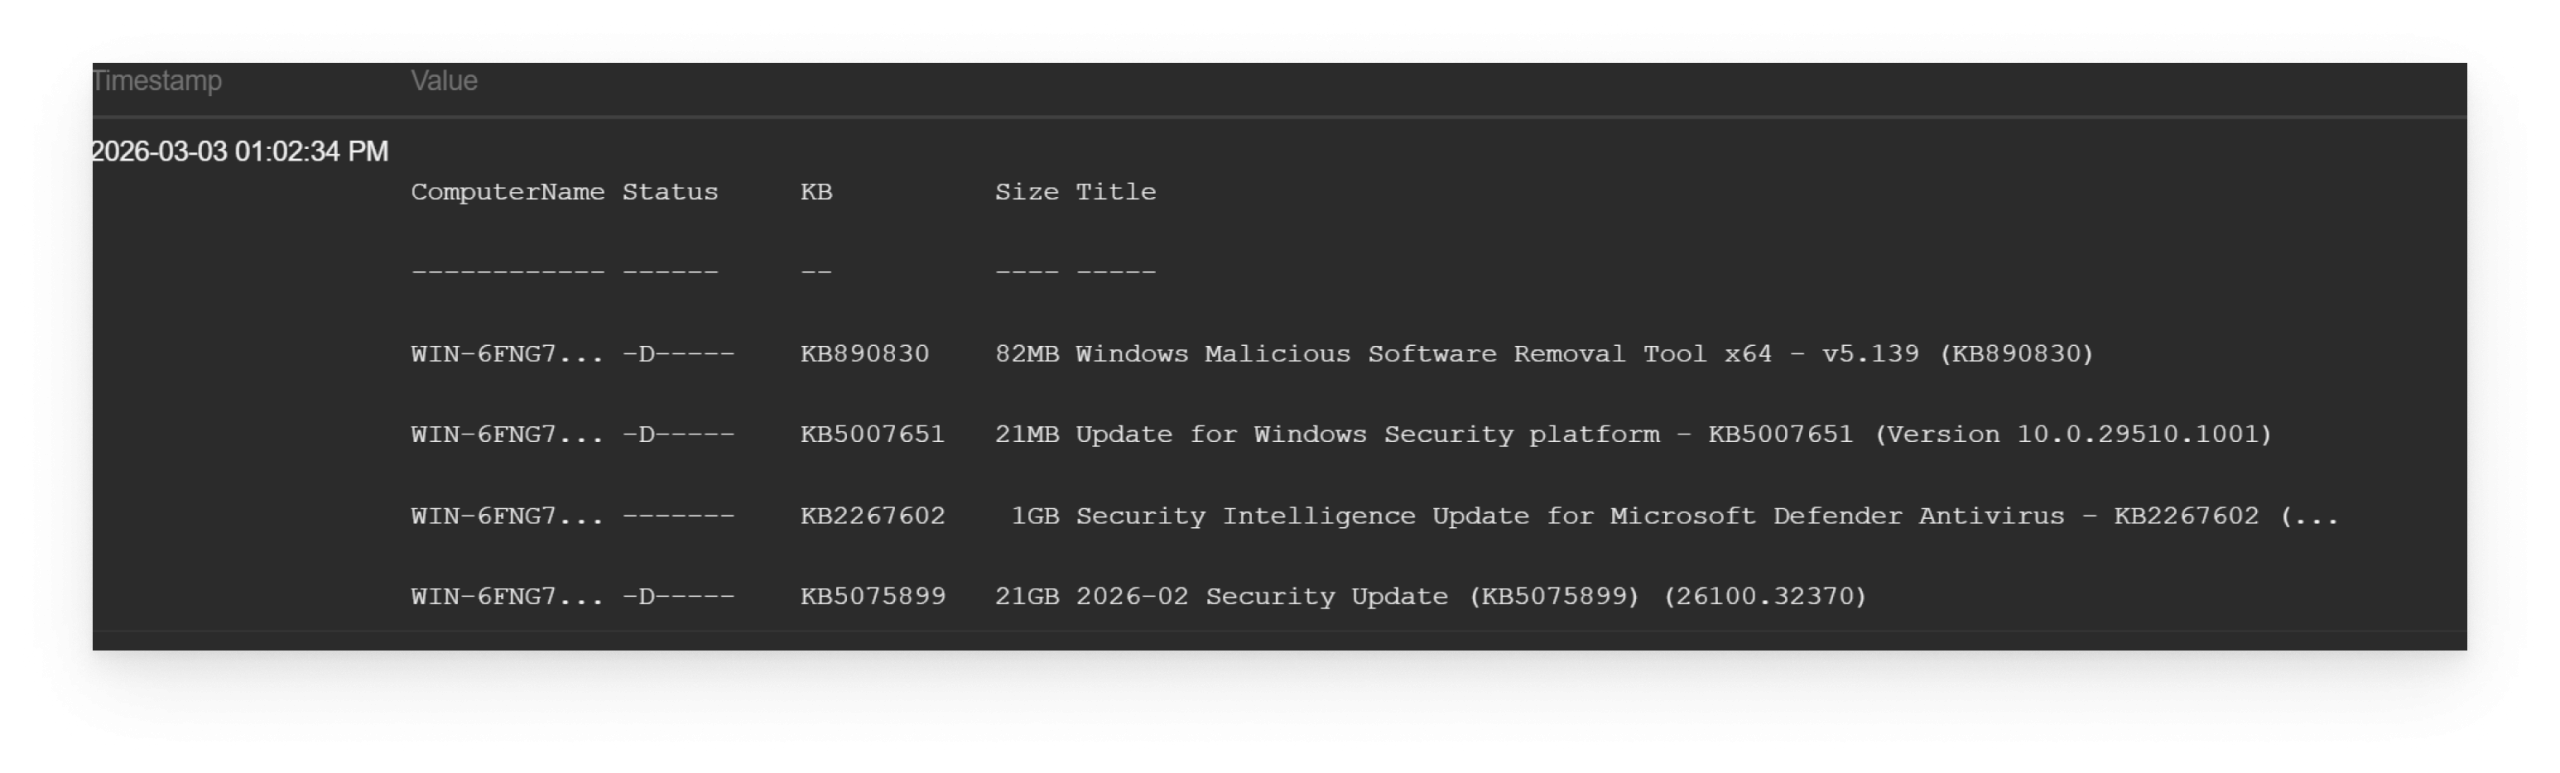
For example, we can use PowerShell to get a list of pending Windows updates:
A User Parameter can point at a PowerShell script to collect additional information in Windows environments
Native Zabbix features such as preprocessing and dependent items can be applied to the collected data to transform or extract the required values or utilize low-level discovery features to automatically create items and triggers based on the ouput of the script.
Finally, the collected data can be used to create different views of your Windows server resource usage, application states and any other collected metrics.
Large selection of dashboard widgets enable Zabbix users to create Windows dashboards for different use cases
It’s nasty, but it requires physical access to the computer:
The exploit, named YellowKey, was published earlier this week by a researcher who goes by the alias Nightmare-Eclipse. It reliably bypasses default Windows 11 deployments of BitLocker, the full-volume encryption protection Microsoft provides to make disk contents off-limits to anyone without the decryption key, which is stored in a secured piece of hardware known as a trusted platform module (TPM). BitLocker is a mandatory protection for many organizations, including those that contract with governments.
Slashdot thread. And here’s Nightmare-Eclipse’s GitHub account.
Microsoft gives the FBI the ability to decrypt BitLocker in response to court orders: about twenty times per year.
It’s possible for users to store those keys on a device they own, but Microsoft also recommends BitLocker users store their keys on its servers for convenience. While that means someone can access their data if they forget their password, or if repeated failed attempts to login lock the device, it also makes them vulnerable to law enforcement subpoenas and warrants.
After twenty-six years, Microsoft is finally upgrading the last remaining instance of the encryption algorithm RC4 in Windows.
of the most visible holdouts in supporting RC4 has been Microsoft. Eventually, Microsoft upgraded Active Directory to support the much more secure AES encryption standard. But by default, Windows servers have continued to respond to RC4-based authentication requests and return an RC4-based response. The RC4 fallback has been a favorite weakness hackers have exploited to compromise enterprise networks. Use of RC4 played a key role in last year’s breach of health giant Ascension. The breach caused life-threatening disruptions at 140 hospitals and put the medical records of 5.6 million patients into the hands of the attackers. US Senator Ron Wyden (D-Ore.) in September called on the Federal Trade Commission to investigate Microsoft for “gross cybersecurity negligence,” citing the continued default support for RC4.
Last week, Microsoft said it was finally deprecating RC4 and cited its susceptibility to Kerberoasting, the form of attack, known since 2014, that was the root cause of the initial intrusion into Ascension’s network.
Fun fact: RC4 was a trade secret until I published the algorithm in the second edition of Applied Cryptography in 1995.
This article gives a good rundown of the security risks of Windows Recall, and the repurposed copyright protection took that Signal used to block the AI feature from scraping Signal data.
For a long time, we have been focusing a lot on the hardware costs of new processors but missing the virtualization license costs. Part of that is simply due to the number of virtualization licenses and support models. Recently, we purchased the most popular barebones server and the most popular server processor on Newegg to […]
A malware campaign uses the unusual method of locking users in their browser’s kiosk mode to annoy them into entering their Google credentials, which are then stolen by information-stealing malware.
Specifically, the malware “locks” the user’s browser on Google’s login page with no obvious way to close the window, as the malware also blocks the “ESC” and “F11” keyboard keys. The goal is to frustrate the user enough that they enter and save their Google credentials in the browser to “unlock” the computer.
Once credentials are saved, the StealC information-stealing malware steals them from the credential store and sends them back to the attacker.
I’m sure this works often enough to be a useful ploy.
The press is reporting a critical Windows vulnerability affecting IPv6.
As Microsoft explained in its Tuesday advisory, unauthenticated attackers can exploit the flaw remotely in low-complexity attacks by repeatedly sending IPv6 packets that include specially crafted packets.
Microsoft also shared its exploitability assessment for this critical vulnerability, tagging it with an “exploitation more likely” label, which means that threat actors could create exploit code to “consistently exploit the flaw in attacks.”
Details are being withheld at the moment. Microsoft strongly recommends patching now.
Interesting attack based on malicious pre-OS logo images:
LogoFAIL is a constellation of two dozen newly discovered vulnerabilities that have lurked for years, if not decades, in Unified Extensible Firmware Interfaces responsible for booting modern devices that run Windows or Linux….
The vulnerabilities are the subject of a coordinated mass disclosure released Wednesday. The participating companies comprise nearly the entirety of the x64 and ARM CPU ecosystem, starting with UEFI suppliers AMI, Insyde, and Phoenix (sometimes still called IBVs or independent BIOS vendors); device manufacturers such as Lenovo, Dell, and HP; and the makers of the CPUs that go inside the devices, usually Intel, AMD or designers of ARM CPUs….
As its name suggests, LogoFAIL involves logos, specifically those of the hardware seller that are displayed on the device screen early in the boot process, while the UEFI is still running. Image parsers in UEFIs from all three major IBVs are riddled with roughly a dozen critical vulnerabilities that have gone unnoticed until now. By replacing the legitimate logo images with identical-looking ones that have been specially crafted to exploit these bugs, LogoFAIL makes it possible to execute malicious code at the most sensitive stage of the boot process, which is known as DXE, short for Driver Execution Environment.
“Once arbitrary code execution is achieved during the DXE phase, it’s game over for platform security,” researchers from Binarly, the security firm that discovered the vulnerabilities, wrote in a whitepaper. “From this stage, we have full control over the memory and the disk of the target device, thus including the operating system that will be started.”
From there, LogoFAIL can deliver a second-stage payload that drops an executable onto the hard drive before the main OS has even started.
It’s an interesting vulnerability. Corporate buyers want the ability to display their own logos, and not the logos of the hardware makers. So the ability has to be in the BIOS, which means that the vulnerabilities aren’t being protected by any of the OS’s defenses. And the BIOS makers probably pulled some random graphics library off the Internet and never gave it a moment’s thought after that.
An impressive array of hacks were demonstrated at the first day of the Pwn2Own conference in Vancouver:
On the first day of Pwn2Own Vancouver 2023, security researchers successfully demoed Tesla Model 3, Windows 11, and macOS zero-day exploits and exploit chains to win $375,000 and a Tesla Model 3.
The first to fall was Adobe Reader in the enterprise applications category after Haboob SA’s Abdul Aziz Hariri (@abdhariri) used an exploit chain targeting a 6-bug logic chain abusing multiple failed patches which escaped the sandbox and bypassed a banned API list on macOS to earn $50,000.
The STAR Labs team (@starlabs_sg) demoed a zero-day exploit chain targeting Microsoft’s SharePoint team collaboration platform that brought them a $100,000 reward and successfully hacked Ubuntu Desktop with a previously known exploit for $15,000.
Synacktiv (@Synacktiv) took home $100,000 and a Tesla Model 3 after successfully executing a TOCTOU (time-of-check to time-of-use) attack against the Tesla-Gateway in the Automotive category. They also used a TOCTOU zero-day vulnerability to escalate privileges on Apple macOS and earned $40,000.
Oracle VirtualBox was hacked using an OOB Read and a stacked-based buffer overflow exploit chain (worth $40,000) by Qrious Security’s Bien Pham (@bienpnn).
Last but not least, Marcin Wiązowski elevated privileges on Windows 11 using an improper input validation zero-day that came with a $30,000 prize.
The con’s second and third days were equally impressive.
A critical code-execution vulnerability in Microsoft Windows was patched in September. It seems that researchers just realized how serious it was (and is):
Like EternalBlue, CVE-2022-37958, as the latest vulnerability is tracked, allows attackers to execute malicious code with no authentication required. Also, like EternalBlue, it’s wormable, meaning that a single exploit can trigger a chain reaction of self-replicating follow-on exploits on other vulnerable systems. The wormability of EternalBlue allowed WannaCry and several other attacks to spread across the world in a matter of minutes with no user interaction required.
But unlike EternalBlue, which could be exploited when using only the SMB, or server message block, a protocol for file and printer sharing and similar network activities, this latest vulnerability is present in a much broader range of network protocols, giving attackers more flexibility than they had when exploiting the older vulnerability.
[…]
Microsoft fixed CVE-2022-37958 in September during its monthly Patch Tuesday rollout of security fixes. At the time, however, Microsoft researchers believed the vulnerability allowed only the disclosure of potentially sensitive information. As such, Microsoft gave the vulnerability a designation of “important.” In the routine course of analyzing vulnerabilities after they’re patched, Palmiotti discovered it allowed for remote code execution in much the way EternalBlue did. Last week, Microsoft revised the designation to critical and gave it a severity rating of 8.1, the same given to EternalBlue.
Yet another article about cyber-weapons arms manufacturers and their particular supply chain. This one is about Windows and Adobe Reader zero-day exploits sold by an Austrian company named DSIRF.
There’s an entire industry devoted to undermining all of our security. It needs to be stopped.
If you plug a Razer peripheral (mouse or keyboard, I think) into a Windows 10 or 11 machine, you can use a vulnerability in the Razer Synapse software — which automatically downloads — to gain SYSTEM privileges.
It should be noted that this is a local privilege escalation (LPE) vulnerability, which means that you need to have a Razer devices and physical access to a computer. With that said, the bug is so easy to exploit as you just need to spend $20 on Amazon for Razer mouse and plug it into Windows 10 to become an admin.
Check Point has evidence that (probably government affiliated) Chinese hackers stole and cloned an NSA Windows hacking tool years before (probably government affiliated) Russian hackers stole and then published the same tool. Here’s the timeline:
The timeline basically seems to be, according to Check Point:
2013: NSA’s Equation Group developed a set of exploits including one called EpMe that elevates one’s privileges on a vulnerable Windows system to system-administrator level, granting full control. This allows someone with a foothold on a machine to commandeer the whole box.
2014-2015: China’s hacking team code-named APT31, aka Zirconium, developed Jian by, one way or another, cloning EpMe.
Early 2017: The Equation Group’s tools were teased and then leaked online by a team calling itself the Shadow Brokers. Around that time, Microsoft cancelled its February Patch Tuesday, identified the vulnerability exploited by EpMe (CVE-2017-0005), and fixed it in a bumper March update. Interestingly enough, Lockheed Martin was credited as alerting Microsoft to the flaw, suggesting it was perhaps used against an American target.
Mid 2017: Microsoft quietly fixed the vulnerability exploited by the leaked EpMo exploit.
Researchers found, and Microsoft has patched, a vulnerability in Windows Defender that has been around for twelve years. There is no evidence that anyone has used the vulnerability during that time.
The flaw, discovered by researchers at the security firm SentinelOne, showed up in a driver that Windows Defender — renamed Microsoft Defender last year — uses to delete the invasive files and infrastructure that malware can create. When the driver removes a malicious file, it replaces it with a new, benign one as a sort of placeholder during remediation. But the researchers discovered that the system doesn’t specifically verify that new file. As a result, an attacker could insert strategic system links that direct the driver to overwrite the wrong file or even run malicious code.
It isn’t unusual that vulnerabilities lie around for this long. They can’t be fixed until someone finds them, and people aren’t always looking.
The collective thoughts of the interwebz
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.