In Finland, where I live, spring has arrived. The snow has melted, and the trees have grown their first buds. But I don’t get my hopes high, as usually around Easter we have what is called takatalvi. Takatalvi is a Finnish world that means that the winter returns unexpectedly in the spring.
Last Week’s Launches Here are some launches that got my attention during the previous week.
AWS Batch – AWS Batch now allows you to configure ephemeral storage up to 200GiB on AWS Fargate type jobs. With this launch, you no longer need to limit the size of your data sets or the size of the Docker images to run machine learning inference.
Application Load Balancer – Application Load Balancer (ALB) now supports Transport Layer Security (TLS) protocol version 1.3, enabling you to optimize the performance of your application while keeping it secure. TLS 1.3 on ALB works by offloading encryption and decryption of TLS traffic from your application server to the load balancer.
Other AWS News Some other updates and news that you may have missed:
I read the post Implementing an event-driven serverless story generation application with ChatGPT and DALL-E a few days ago, and since then I have been reading my child a lot of AI-generated stories. In this post, David Boyne, explains step by step how you can create an event-driven serverless story generation application. This application produces a brand-new story every day at bedtime with images, which can be played in audio format.
Podcast Charlas Técnicas de AWS – If you understand Spanish, this podcast is for you. Podcast Charlas Técnicas is one of the official AWS podcasts in Spanish, and every other week there is a new episode. The podcast is meant for builders, and it shares stories about how customers have implemented and learned AWS services, how to architect applications, and how to use new services. You can listen to all the episodes directly from your favorite podcast app or at AWS Podcasts en español.
AWS open-source news and updates – The open source newsletter is curated by my colleague Ricardo Sueiras to bring you the latest open-source projects, posts, events, and more.
Upcoming AWS Events Check your calendars and sign up for the AWS Summit closest to your city. AWS Summits are free events that bring the local community together, where you can learn about different AWS services.
External vendor APIs can help organizations streamline operations, reduce costs, and provide better services to their customers. But many challenges exist in integrating with third-party services such as security, reliability, and cost.
Organizations must ensure their systems can handle performance issues or downtime. In some cases, calling an external API may have associated costs such as licensing fees. If a contract exists with the external API vendor to adhere to maximum Requests Per Second (RPS), the system needs to adapt accordingly.
In this blog post, we show you how to build an architecture to invoke an external vendor API using AWS Step Functions, with specific guidance on reliability.
This orchestration is applicable to any industry that relies on technology and data benefitting from external vendor API integration. Examples include e-commerce applications for online retailers integrating with third-party payment gateways, shipping carriers, or applications in the healthcare and banking sectors.
Invoking asynchronous external APIs overview
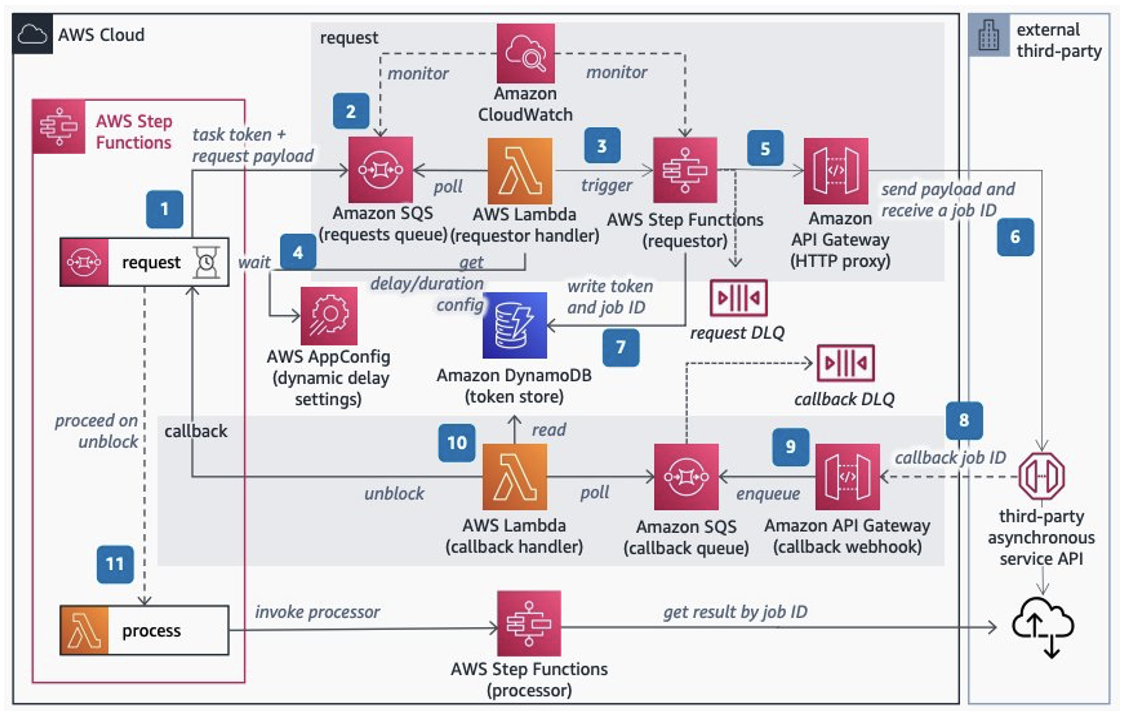
This solution outlines the use of AWS services to build an orchestrator controlling the invocation rate of third-party services that implement the service callback pattern to process long-running jobs. This architecture is also available in the AWS Reference Architecture Diagrams section of the AWS Architecture Center.
As in Figure 1, the architecture gives you the control to feed your calls to an external service according to its maximum RPS contract using Step Functions capabilities. Step Functions pauses main request workflows until you receive a callback from the external system indicating job completion.
Set up Step Functions to handle the lifecycle of long-running requests to the third party. Inside the workflow, add a request step that pauses it using waitForTaskToken as a callback to continue. Set a timeout to throw a timeout error if a callback isn’t received.
Send the task token and request payload to an Amazon Simple Queue Service (Amazon SQS) queue. Use Amazon CloudWatch to monitor its length. Consider adjusting the contract with the third-party service if the queue length grows beyond a soft limit determined on the maximum RPS with the third party.
Optionally, add dynamic delay inside Lambda controlled by AWS AppConfig if the system still needs a lower invocation rate to comply with the contracted RPS.
Step Functions invokes an Amazon API Gateway HTTP proxy API configured with rate limit to comply with the contracted RPS. API Gateway is a safeguard proxy to make sure your system is not breaking the RPS contract while dynamically adjusting the invocation rate parameters.
Invoke the external third-party asynchronous service API sending the payload consumed from the requests queue and receiving the jobID from the service. Send failed requests to the Dead Letter Queue (DLQ) using Amazon SQS.
Store the main workflow’s task token and jobID from the third-party service in an Amazon DynamoDB table. This is used as a mapping to correlate the jobID with the task token.
When the external service completes, receive the completed jobID in a callback webhook endpoint implemented with API Gateway.
Transform the external callbacks with API Gateway mapping templates, add the payload and jobID to an Amazon SQS queue, and respond immediately to the caller.
Use Lambda to poll the callback Amazon SQS queue, then query the token stored. Use the token to unblock the waiting workflow by calling SendTaskSuccess and the callback DLQ to store failed messages.
On the main workflow, pass the jobID to the next step and invoke a Step Functions processor to fetch the third-party results. Finally, process the external service’s results.
Controlling external API invocation rates
To comply with third-party RPS contracts, adopt a mechanism to control your system’s invocation rate. The rate of polling the messages from the request Amazon SQS (or step 3 in the architecture) directly impacts your invocation rate.
Different parameters can be used to control the invocation rate for Lambda with Amazon SQS as its trigger “event source,” such as:
Batch size: The number of records to send to the function in each batch. For a standard queue, this can be up to 10,000 records. For a first-in, first-out (FIFO) queue, the maximum is 10. Using batch size on its own will not limit the invocation rate. It should be used in conjunction with other parameters such as reserved concurrency or maximum concurrency.
Batch window: The maximum amount of time to gather records before invoking the function, in seconds. This applies only to standard queues.
Maximum concurrency: Sets limits on the number of concurrent instances of the function that an Amazon SQS event source can invoke. Maximum concurrency is an event source-level setting.
Trigger configuration is shown in Figure 2.
Figure 2. Configuration parameters for triggering Lambda
Other Lambda configuration parameters can also be used to control the invocation rate, such as:
Reserved concurrency: Guarantees the maximum number of concurrent instances for the function. When a function has reserved concurrency, no other function can use that concurrency. This can be used to limit and reduce the invocation rate.
Provisioned concurrency: Initializes a requested number of execution environments so that they are prepared to respond immediately to your function’s invocations. Note that configuring provisioned concurrency incurs charges to your AWS account.
These additional Lambda configuration parameters are shown here in Figure 3.
Figure 3. Lambda concurrency configuration options – Reserved and Provisioned
Maximizing your external API architecture
During this architecture implementation, consider some use cases to ensure that you are building a mature orchestrator.
Let’s explore some examples:
If the external system fails to respond to the API request in step 8, a timeout exception will occur at step 1. A sensible timeout should be configured in the main state machine in step 1. The timeout value should consider the maximum response time of the external system.
Dynamic delay inside the Lambda function—as mentioned in step 4—should only be used temporarily for burst traffic. If the external party has a very low RPS contract, consider other alternatives to introduce delay.
For example, Amazon EventBridge Scheduler can be used to trigger the Lambda function at regular intervals to consume the messages from Amazon SQS. This avoids costs for the idle/waiting state of your Lambda functions.
Conclusion
This blog post discusses how to build end-to-end orchestration to manage a request’s lifecycle, five different parameters to control invocation rate of third-party services, and throttle calls to external service API per maximum RPS contract.
We also consider use cases on using error handling capabilities in Step Functions and monitor systems with CloudWatch. In addition, this architecture adopts fully managed AWS Serverless services, removing the undifferentiated heavy lifting in building highly available, reliable, secure, and cost-effective systems in AWS.
Cloudflare’s commitment to building the most compelling and easy-to-use SASE platform on the market has led to significant growth over the past year. Cloudflare One services have seen the fastest adoption among our customers, with a 3x increase in partner bookings and a 70% YoY increase in transacting partners. Partners consistently cite the simplicity of our platform, our innovation, and our global network as key differentiators that are driving strong customer demand.
To continue building on this momentum and deliver required services that our customers may require, we previously announced the creation of our new specialization track for Authorized Services Delivery Partners (ASDP) as part of our efforts to continue growing our partnership program.
Cloudflare’s Authorized Services Delivery Partner track is designed to authorize partners that meet our high standards for professional services delivery around Cloudflare One. Partners who undergo the rigorous technical validation process and meet the criteria for security, performance, and reliability of their services delivery capabilities are designated as Cloudflare Authorized Service Delivery Partners. This designation provides a variety of benefits, including access to Cloudflare One sourced opportunities requiring services, access to named Cloudflare One Service Delivery Managers, and access to special partner incentive funds designed to ensure that authorized partner services are actively used in Cloudflare One customer engagements.
In addition, we’re pleased to announce that our authorized partners, with their deep skills and capabilities, will play a critical role in the Descaler Program. Authorized partners will work closely with customers to understand their unique needs and goals, and provide strategic consultation and technical expertise throughout the migration journey. Authorized partners will also have the opportunity to leverage the Descaler toolkit to automatically export settings and configurations of deployed Zscaler products to be migrated into Cloudflare, enabling a frictionless transition to Cloudflare One.
Since launch, Cloudflare One’s Authorized Services Delivery Partner track is having a notable impact on our partner ecosystem, providing a framework for partners to showcase their expertise in Cloudflare One services and delivering high-quality professional and managed services to customers. The program has attracted a diverse range of partners who bring different skillsets and expertise to the table, including Zero Trust security assessments, network transformation, and advisory and migration services, among others. By authorizing partners who meet our high standards for services delivery, we are providing customers with a clear path to trusted advisors who can help them navigate their journey to a cloud-delivered SASE architecture.
We are thrilled to now announce the first partners who have achieved the ASDP designation.
CDS enables strategic change by partnering with best-in-class technology providers like Cloudflare, delivering the professional services wrap that ensures that organisations get the best value from their chosen technology including strategic guidance, implementation, architectural governance and for clients with complex needs, a managed service. CDS’ approach ensures Cloudflare services are continuously optimised to the highest standards and that clients achieve the fullest value from their licence. CDS offers a Cloudflare certified team of experts with genuine market experience, who can solve significant security challenges while allowing clients to see their projects from multiple angles, encouraging more secure, creative and innovative solutions
Miguel Ferreira, Head of Cloud Services for CDS says:
“We are thrilled to be one of the first partners in EMEA to achieve Cloudflare’s ‘Authorized Service Delivery Partner’ status. Being a part of this program is critical for us because it validates our commitment to excellence and provides us with the tools and support we need to deliver successful engagements. At CDS, we consider ourselves to be the champions of our clients, helping them to navigate and enable change. Part of this is giving our clients confidence to make significant technology decisions that could make or break their aspirations for digital transformation. Being able to rely on a professional services partner with, in this case, Cloudflare Authorized Services Delivery Partner status, significantly reduces the risk associated with these types of decisions. We look forward to working closely with the Cloudflare team to deliver innovative solutions and exceptional customer experiences.”
Primary Guard provides a leading-edge cybersecurity solution that specializes in IT & network security services in Southeast Asia, delivering fast and secured websites through tailor-made solutions that comply with cybersecurity best practices and performance requirements such as DDoS protection and DDoS mitigation, business endpoint protection, and access control management. They are the award winner for 2020 Cloudflare APJC Partner Champions under Partner System Engineer of the Year category. Being a leader in cybersecurity service provider in ASEAN region, their Lead Security Consultant is also awarded as Cloudflare Community MVP for 2021-2023.
Commenting on their designation as an Authorized Service Partner, Johary Mustapha, CEO of Primary Guard says:
“We are thrilled to be a part of the Authorized Service Delivery Partners program which recognizes Primary Guard’s expertise in zero-trust solutions and adherence to industry best practices. Being a part of this program truly validates our commitment to excellence and provides us with the tools and support we need to deliver successful client engagements across industries and of all sizes. We look forward to working closely with the Cloudflare team to deliver more innovative cybersecurity solutions and exceptional customer experiences.”
AZ Asia-Pacific is a full-fledged Cyber Security Distribution Services Hub headquartered in Singapore with offices and operations in Malaysia, Thailand, Philippines, Indonesia, China and Hong Kong that works with the best of breed System Integrators and Service Providers across the Asia-Pacific Region. AZ AP focus is on delivering quality Solutions and Services in Cyber Security Technology, which includes Zero Trust Network Architecture, Application Security, Cloud and Network Security.
According to Jeremy Woo – Founder & CEO of AZ-AP:
“We are honored to be included in the prestigious Authorized Service Delivery Partners program. This recognition reflects our proficiency in zero trust solutions and our dedication to upholding industry standards, while also providing us with invaluable access to exclusive benefits and resources that will enable us to better support our partners. Joining this program is essential for us because it validates our unwavering commitment to providing outstanding service and equips us with the necessary tools and support to deliver successful engagements. We eagerly anticipate collaborating with the Cloudflare team to deliver ground breaking solutions and unparalleled customer experiences.”
LAYER8 is a company fully focused on the business of information security and compliance management. With more than 80 highly specialized professionals, they deliver solutions that add value to the business and simplify the adoption of information security in organizations around the world. Cloudflare Zero Trust Platform embodies these qualities with its simple and flexible yet highly secure architecture.
Fernando Cardoso, COO at Layer8 says:
“Being part of the Authorized Service Delivery Partners program not only acknowledges our proficiency in zero trust solutions but also equips us with the necessary resources and support to carry out successful projects, enabling us to serve our clients more effectively. This partnership with Cloudflare will certainly strengthen our focus on innovation and business value creation activities.”
Opticca Security is a boutique consulting firm specialized in Edge, Cloud, DevOps and Application Security. Supporting Mid, Large and Enterprise organizations across North America integrate & automate security controls across multiple facets of their IT architecture and software development pipelines. Opticca Security has been a certified Cloudflare Solution reseller and Services partner since 2019 and continues to benefit from Cloudflare’s innovative technology stack, coupled with Opticca Security’s expertise regarding Application Modernization and DevSecOps enablement.
Managing Director Joey Campione from Opticca Security offers their perspective on their achievement, stating that:
“We are very excited to be involved with Cloudflare’s Authorized Services Delivery Partner program, as it will permit us to continue to drive superior security and performance to our existing and future clients. Cloudflare’s continuous investments in platform innovation and the partner ecosystems is allowing us to help our customers be more efficient and competitive by modern standards”.
These partners have demonstrated their expertise in Cloudflare One services and their commitment to delivering high-quality services to customers. We congratulate them on this achievement and look forward to continuing to work with them to deliver exceptional value to our mutual customers.
Roadmap
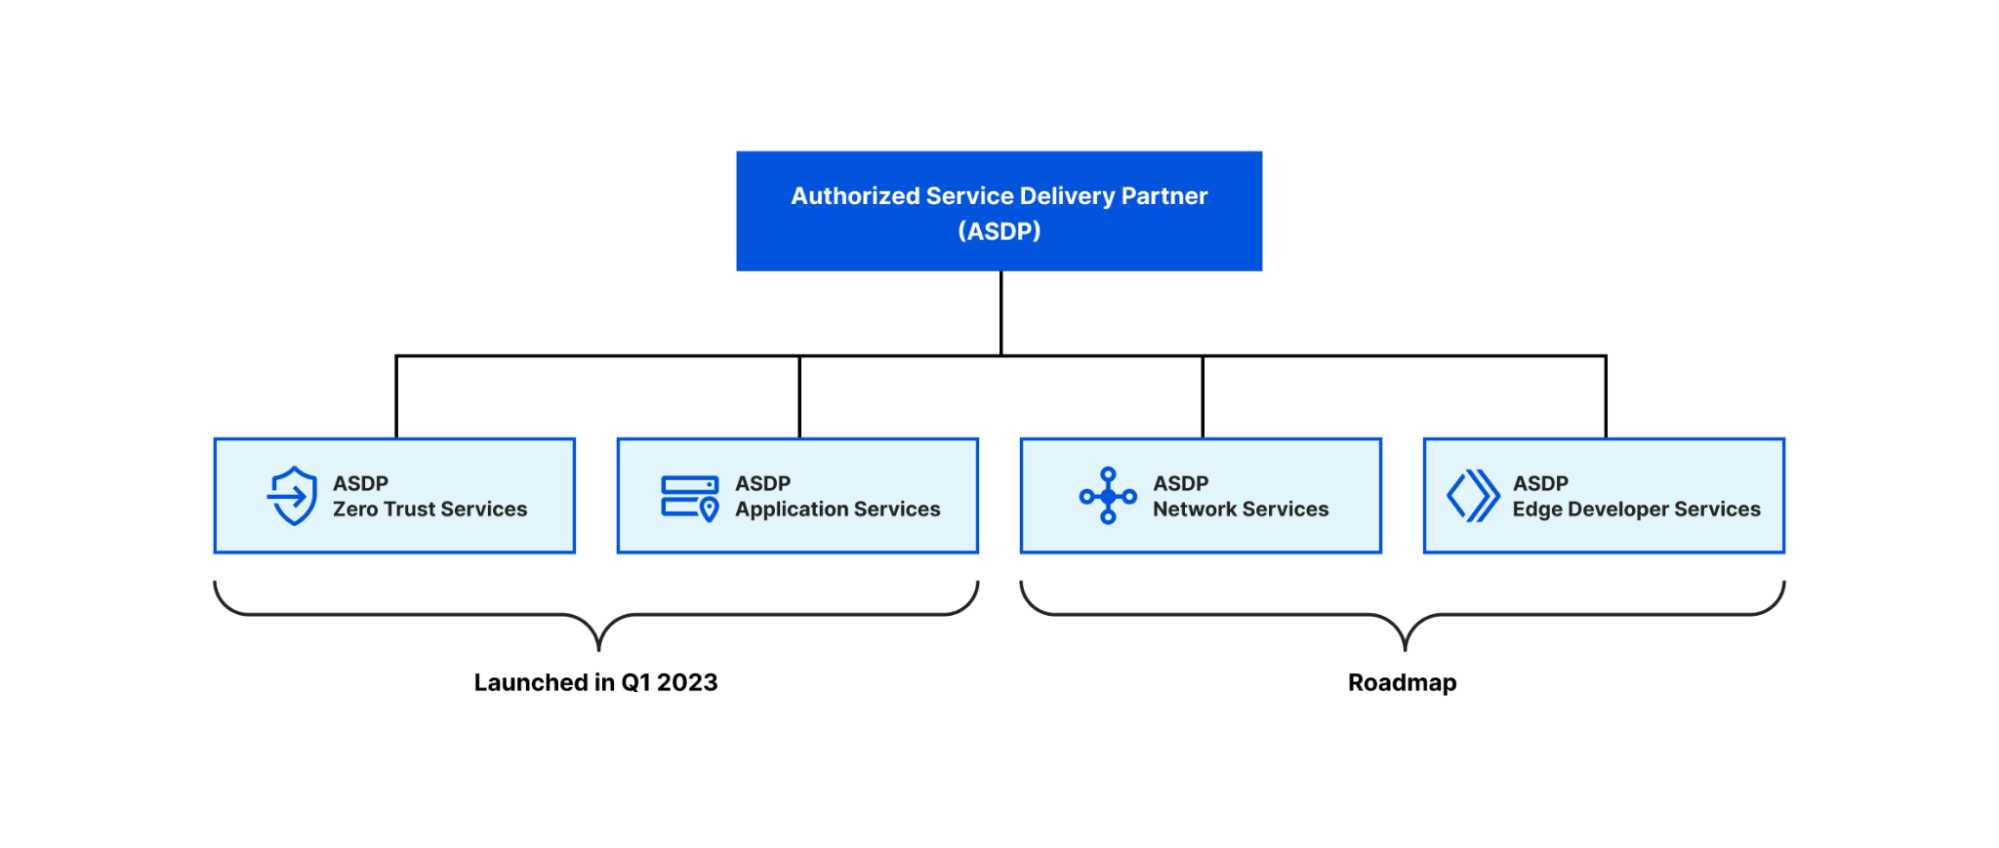
As of today, Authorized Service Delivery Partner Program has two specializations: ASDP Zero Trust Services and ASDP Application Services. We are also planning to launch two additional specializations in the near future: ASDP Network Services and ASDP Edge Developer Services. Our goal is to work closely with our partners to develop comprehensive solutions that deliver real value to our customers. The launch of additional specializations will provide even more opportunities for our partners to differentiate themselves in the market.
Conclusion
At Cloudflare, we remain committed to building a strong and strategic network of channel partners who can help us deliver the best possible services and solutions to our customers. We are excited to continue growing our partnership program and to work with our ASDP partners to deliver exceptional value and results. If you are a prospective partner interested in the ASDP track, please see our Cloudflare Authorized Service Delivery Partner validation checklist for details on the application process. If you are an existing Cloudflare partner, please reach out to your named Channel Account Manager for additional information.
Иван Христанов е предприемач и инвеститор. В 47-то Народно събрание той бе народен представител от Област Плевен от квотата на ПП “Продължаваме промяната”. От декември 2021 г. до август 2022…
An impressive array of hacks were demonstrated at the first day of the Pwn2Own conference in Vancouver:
On the first day of Pwn2Own Vancouver 2023, security researchers successfully demoed Tesla Model 3, Windows 11, and macOS zero-day exploits and exploit chains to win $375,000 and a Tesla Model 3.
The first to fall was Adobe Reader in the enterprise applications category after Haboob SA’s Abdul Aziz Hariri (@abdhariri) used an exploit chain targeting a 6-bug logic chain abusing multiple failed patches which escaped the sandbox and bypassed a banned API list on macOS to earn $50,000.
The STAR Labs team (@starlabs_sg) demoed a zero-day exploit chain targeting Microsoft’s SharePoint team collaboration platform that brought them a $100,000 reward and successfully hacked Ubuntu Desktop with a previously known exploit for $15,000.
Synacktiv (@Synacktiv) took home $100,000 and a Tesla Model 3 after successfully executing a TOCTOU (time-of-check to time-of-use) attack against the Tesla-Gateway in the Automotive category. They also used a TOCTOU zero-day vulnerability to escalate privileges on Apple macOS and earned $40,000.
Oracle VirtualBox was hacked using an OOB Read and a stacked-based buffer overflow exploit chain (worth $40,000) by Qrious Security’s Bien Pham (@bienpnn).
Last but not least, Marcin Wiązowski elevated privileges on Windows 11 using an improper input validation zero-day that came with a $30,000 prize.
The con’s second and third days were equally impressive.
Опасявам се, че както вървят нещата, седмичният ни бюлетин ще се превърне в многосезонен сериал с един основен претендент за престола на главния герой. И то какъв герой – истински херой в развитие и в полёте!
В началото зрителите на сериала го наричахме помежду си с безобидни, смешновати прозвища, навяващи далечни асоциации с капитан Дългия чорап, по случайност свише (морска буря) станал безгрижен крал на безгрижен остров. Както се досещате обаче, тези асоциации са твърде повърхностни, защото в нашия „чунга-чанга“ сериал нито хероят лётчик (пардон, капитан) застава случайно начело на държавния кораб, нито пък България е остров (нищо че хероят всячески се опитва да я откъсне от европейската суша), още по-малко пък безгрижен.
И така, напоследък хероят расте в чин всяка седмица и съвсем заслужено си печели нови прозвища, които вече свързваме с един друг тип герои. С ло-ши-те! Например с дон Домат – злодей и деребей, но всъщност просто раболепен управител и иконом на замъка. Или с троянския кон, който в нашия случай повече прилича на заинатено магаре (с фуражка) на мост.
Притесненията ни обаче са свързани с възможностите за развитие на този толкова ресурсен персонаж (до финалния сезон на сериала през 2027 г. има доста време). И с опасността да заприлича на Онзи-който-не-бива-да-се-назовава или Ти-знаеш-кой… И трайно да ни свърже и обвърже със „смъртножадните“ на изток. (Като споменах изток, ето един филм на „Свободна Европа“ за руската следа в „Неразкритите взривове в сянката на войната на Русия в Украйна“. Изгледайте го, струва си.)
Та на този етап нашият херой лётчик все още диша прахта на Волдемор, но затова пък все по-успешно конкурира Бойко Борисов (и други одиозни фигури в политическото ни настояще). Повече за тези любопитни сродства четете в чудесния анализ на Емилия Милчева „Радев е Борисов и половина“.
На фона на поредната порция президентски гафове (думата „гаф“ в случая е милостиво-мека за срама, който всинца берем) Александър Нуцов насочва вниманието ни към „Геополитиката на Северно море“ и ключовата му роля на един от основните маршрути за диверсификация на газовите доставки от Русия, следователно залог за енергийната стабилност в Европа.
Не само защото все още е март, продължаваме с осмомартенската тема в разказа на Светла Енчева за „Женското лице на бедността в България“. В материала звучат думите на 4 жени, чиито съдби доказват тъжната хипотеза, че бедността има свойството да се възпроизвежда.
В самия край на миналата седмица научихме за смъртта на голямата хърватска писателка с български корен и скиталческа душа Дубравка Угрешич. Загубата на светъл ум в мрачни времена е не просто скръбна, а дълбоко обезкуражаваща. Дано великолепните ѝ книги оцелеят в този свят, който непрестанно забравя уж научените уроци. Именно за оцеляването на високата култура, вярата и възможността за чудо в контекста на все по-ускорената комодификация четем в интервюто с друг един светъл ум, поляка Кшищов Зануси, с когото Стефан Гончаров разговаря по време на 27-мото издание на „София Филм Фест“ и по повод най-новия филм на режисьора „Идеалното число“.
В тазседмичната си литературна рубрика пък Зорница Христова ни запознава с романа на Людмил Тодоров „Смяна на оптиката“, с изследването на проф. Цочо Бояджиев „Зимата през Средновековието“ и с новата стихосбирка на Людмила Миндова „Чуден свят“. Три разнородови и разножанрови книги, които обаче изненадват с различната си тяга към реалността и автентиката на отношенията ни, на живота ни в настоящето, на миналото и историите, от които сме направени.
Без никаква връзка с височайшето посещение на Си Цзинпин при Путин, завършваме месеца и посрещаме пролетта със стихотворението „Устните бясно танцуват“ на съвременния китайски поет Ю Дзиен в превод на Веселин Карастойчев. Избрахме го заради снарядите страст и горест, избухнали в текста – знак, че и този път победата е на страната на пролетта.
“When a squid ends up chipping what’s called its ring tooth, which is the nail underneath its tentacle, it needs to regrow that tooth very rapidly, otherwise it can’t claw its prey,” he explains.
This was intriguing news and it sparked an idea in Hopkins lab where he’d been trying to figure out how to store and transmit heat.
“It diffuses in all directions. There’s no way to capture the heat and move it the way that you would electricity. It’s just not a fundamental law of physics.”
[…]
The tiny brown batteries he mentions are about the size of a chiclet, and Hopkins says it will take a decade or more to create larger batteries that could have commercial value.
As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.