Hacking Digital License Plates

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/12/hacking-digital-license-plates.html

Not everything needs to be digital and “smart.” License plates, for example:

Josep Rodriguez, a researcher at security firm IOActive, has revealed a technique to “jailbreak” digital license plates sold by Reviver, the leading vendor of those plates in the US with 65,000 plates already sold. By removing a sticker on the back of the plate and attaching a cable to its internal connectors, he’s able to rewrite a Reviver plate’s firmware in a matter of minutes. Then, with that custom firmware installed, the jailbroken license plate can receive commands via Bluetooth from a smartphone app to instantly change its display to show any characters or image.

[…]

Because the vulnerability that allowed him to rewrite the plates’ firmware exists at the hardware level­—in Reviver’s chips themselves—Rodriguez says there’s no way for Reviver to patch the issue with a mere software update. Instead, it would have to replace those chips in each display.

The whole point of a license plate is that it can’t be modified. Why in the world would anyone think that a digital version is a good idea?

How DeNA Co., Ltd. accelerated anonymized data quality tests up to 100 times faster using Amazon Redshift Serverless and dbt

Post Syndicated from Momota Sasaki original https://aws.amazon.com/blogs/big-data/how-dena-co-ltd-accelerated-anonymized-data-quality-tests-up-to-100-times-faster-using-amazon-redshift-serverless-and-dbt/

This blog was co-authored by DeNA Co., Ltd. and Amazon Web Services Japan.

DeNA Co., Ltd. (DeNA) engages in a variety of businesses, from games and live communities to sports & the community and healthcare & medical, under our mission to delight people beyond their wildest dreams. Among these, the healthcare & medical business handles particularly sensitive data. To comply with their data policies for sensitive data, this healthcare & medical business set the following requirements for their data processing:

  • Process data in compliance with data policies – Mask or delete sensitive data as necessary to transform into anonymized data. Prevent the inclusion of invalid values in categorical data and process data without any data loss.
  • Conduct data quality tests on anonymized data in compliance with data policies – Conduct data quality tests to quickly identify and address data quality issues, maintaining high-quality data at all times.

This post introduces a case study where DeNA combined Amazon Redshift Serverless and dbt (dbt Core) to accelerate data quality tests in their business.

The challenge

Data quality tests require performing 1,300 tests on 10 TB of data monthly. Previously, DeNA ran Python-based batch jobs on Amazon Elastic Compute Cloud (Amazon EC2) to perform these data quality tests. As business and data volume grew over time, DeNA started to face the following challenges:

  • Performance – Data quality tests took days to weeks to complete because engineers hadn’t designed the batch jobs to handle big data.
  • Cost – Costs increased due to the batch job design, particularly for large datasets. The implementation required loading data into memory for processing. When handling large table data, DeNA needed to use large memory-optimized EC2 instances.
  • Maintainability – The batch job implementations varied significantly between engineers, leading to high maintenance overhead, because the required knowledge was siloed among individual engineers.

The switch to Redshift Serverless and dbt

To address these challenges, DeNA decided to adopt Redshift Serverless and dbt (an open source data transformation tool) for the following key reasons:

  • Scalable and cost-effective processing with Redshift Serverless
  • Standardized and maintainable data quality tests with dbt

This decision was made after careful comparison of alternative solutions. DeNA initially considered parallelizing the existing Python-based batch jobs but rejected this approach due to the high maintenance overhead and siloed knowledge associated with the batch jobs. Instead, DeNA decided to use dbt, which DeNA has been using in their healthcare & medical business, and connect it to an AWS service capable of large-scale distributed processing. dbt provides a SQL-first templating engine for repeatable and extensible data transformations, including a data tests feature, which allows verifying data models and tables against expected rules and conditions using SQL. By using dbt, DeNA could standardize the technical stack, implement data quality tests in maintainable SQL, and connect dbt to a managed service for scalable and cost-effective processing.

AWS offers several services that are compatible with dbt, including Amazon Redshift and AWS Glue. DeNA selected Redshift Serverless, primarily due to its serverless nature, optimal cost-performance, and the superior processing performance for structured data typical of a data warehouse service.

Solution overview

DeNA designed the following architecture using AWS serverless services.

The workflow consists of the following high-level steps and key design points:

  1. The source system stores the target data for the data quality tests in Amazon Simple Storage Service (Amazon S3). When new data files are added, Amazon EventBridge invokes an AWS Step Functions state machine (workflow). To make sure all files for target data are delivered, the source system stores a completion file in Amazon S3.
  2. dbt runs on Amazon Elastic Container Service (Amazon ECS) using AWS Fargate, an AWS serverless container service. DeNA selected Amazon ECS because it allows running dbt in a serverless, pay-per-use manner, and DeNA had prior experience developing and operating applications using Amazon ECS. To allow the containers to securely access Redshift Serverless, DeNA used the pass sensitive data to an ECS container feature to pass sensitive credentials that are stored in AWS Secrets Manager to the containers using an ECS task execution IAM role.
  3. DeNA segmented Redshift Serverless into separate workgroups for access control. Operation personnel may need to access the Redshift Serverless database using the Query Editor V2 to investigate issues with data quality tests, while maintaining strict access control. Redshift Serverless allows fine-grained access control to data by using database security features, similar to how the GRANT command is used in database products. However, in this workload, DeNA chose to use AWS Identity and Access Management (IAM) to control access to the workgroups at IAM level. This allowed DeNA to restrict access to specific Redshift Serverless workgroups based on users’ IAM roles, enabling unified management of authorization through IAM. Additionally, by separating the workgroups, DeNA could individually adjust Redshift Processing Units (RPUs) per workgroup, contributing to cost optimization.
  4. Amazon ECS sends execution logs of dbt running to Amazon CloudWatch Logs for observability. DeNA used metric filters to convert the logs into CloudWatch metrics, then created alarms based on these metrics. When triggered, these alarms invoke AWS Lambda functions using Amazon Simple Notification Service (Amazon SNS). The Lambda functions create result reports of dbt running and data quality tests and send them to an internal chat application. DeNA visualizes the results of data quality tests using the elementary CLI, a dbt-based data observability solution. This workflow enables even non-engineers to track data quality status effectively.

Outcomes

DeNA successfully addressed all the challenges they faced by designing the solution and migrating to a new platform:

  • Performance – Improved performance up to 100 times faster by reducing processing time from days or weeks to 1–2 hours. A certain data quality test that previously took 877 minutes now completes in 1 minute, thanks to the large-scale distributed processing capabilities of Redshift Serverless.
  • Cost – Reduced costs by 90% with AWS serverless services. Optimized expenses by incurring costs only for data quality tests.
  • Maintainability – Standardized the technical stack with dbt, eliminating siloed knowledge from custom programs. dbt’s data tests feature simplified the implementation of data quality tests. The elementary CLI improved the observability of data quality tests for non-engineers. AWS serverless services virtually eliminated the operational overhead for managing the workload infrastructure.

Conclusion

This post demonstrated how DeNA was able to securely and efficiently accelerate their data quality tests by combining Redshift Serverless and dbt. This combination is not only effective for DeNA’s use case but also applicable to various business use cases across different industries.

For more information on the combination of Redshift Serverless and dbt, refer to the following resources:


About the Author

Momota Sasaki is an Engineering Manager at DeSC Healthcare, a subsidiary of DeNA. He joined DeNA in 2021 and was seconded to DeSC Healthcare. Since then, he has been consistently involved in the healthcare business, leading and promoting the development and operation of the data platform.

Kaito Tawara is a Data Engineer at DeSC Healthcare, a subsidiary of DeNA, focusing on improving healthcare data platforms. After gaining experience in backend development for web systems and data science, he transitioned to data engineering. He joined DeNA in 2023 and was seconded to DeSC Healthcare. Currently, he works remotely from Nagoya-city, contributing to the enhancement of healthcare data platforms.

Shota Sato is an Analytics Specialist Solution Architect at AWS Japan, focusing on data analytics solutions powered by AWS for digital native business customers.

Top 6 game changers from AWS that redefine streaming data

Post Syndicated from Sai Maddali original https://aws.amazon.com/blogs/big-data/top-6-game-changers-from-aws-that-redefine-streaming-data/

Recently, AWS introduced over 50 new capabilities across its streaming services, significantly enhancing performance, scale, and cost-efficiency. Some of these innovations have tripled performance, provided 20 times faster scaling, and reduced failure recovery times by up to 90%. We have made it nearly effortless for customers to bring real-time context to AI applications and lakehouses.

In this post, we discuss the top six game changers that will redefine AWS streaming data.

Amazon MSK Express brokers: Kafka reimagined for AWS

AWS offers Express brokers for Amazon Managed Streaming for Apache Kafka (Amazon MSK)—a transformative breakthrough for customers needing high-throughput Kafka clusters that scale faster and cost less. With Express brokers, we are reimagining Kafka’s compute and storage decoupling to unlock performance and elasticity benefits. Express brokers offer up to three times more throughput than a comparable standard Apache Kafka broker, virtually unlimited storage, instant storage scaling, compute scaling in minutes vs. hours, and 90% faster recovery from failures compared to standard Kafka brokers. Customers can provision capacity in minutes without complex calculations, benefit from preset Kafka configurations, and scale capacity in a few clicks. Express brokers provide the same low-latency performance as standard Kafka, are 100% native Kafka, and offer key Amazon MSK features. There are no storage limits per broker and you only pay for the storage you use. With Express brokers for Amazon MSK, enterprises can expand their Kafka usage to support even more mission-critical use cases, while keeping both operational overhead and overall infrastructure costs low.

Amazon Kinesis Data Streams On-Demand: Scaling new heights

Amazon Kinesis Data Streams On-Demand makes it uncomplicated for developers to stream gigabytes per second of data without managing capacity or servers. Developers can create a new on-demand data stream or convert an existing data stream to on-demand mode with a single click. Kinesis Data Streams On-Demand now automatically scales to 10 GBps of write throughput and 200 GBps of read throughput per stream, a fivefold increase. Customers will automatically get this fivefold increase in scale without the need to take any action.

Streaming data to Iceberg tables in lakehouses

Enterprises are embracing lakehouses and open table formats such as Apache Iceberg to unlock value from their data. Amazon Data Firehose now supports seamless integration with Iceberg tables on Amazon Simple Storage Service (Amazon S3). Customers can stream data into Iceberg tables in Amazon S3 without any management overhead. Data Firehose compacts small files, minimizing storage inefficiencies and enhancing read performance. Data Firehose also handles schema changes while in flight, to provide consistency across evolving datasets. Because Data Firehose is fully managed and serverless, it scales seamlessly to handle high throughput streaming workloads, providing reliable and fast delivery of data. This capability also makes it straightforward to stream data stored in MSK topics and Kinesis data streams into Iceberg tables, potentially eliminating the need for custom extract, transform, and load (ETL) pipelines. Customers can now bring the power of real-time data to Iceberg tables without any additional effort—a paradigm shift for businesses. Additionally, Kinesis Data Firehose serves as a versatile bridge to stream real-time data from MSK clusters and Kinesis Data Streams into the newly launched Amazon S3 Tables and Amazon SageMaker Lakehouse. This unified approach facilitates more effective data management and analysis, supporting data-driven decision-making across the enterprise.

Unlocking the value of data stored in databases with change replication to Iceberg tables

Delivering database changes into Iceberg tables is emerging as a common pattern. Now in public preview, Data Firehose supports capturing changes made in databases such as PostgreSQL and MySQL and replicating the updates to Iceberg tables on Amazon S3. The integration uses change data capture (CDC) to continuously deliver database updates, eliminating manual processes and reducing operational overhead. Data Firehose automates tasks such as schema alignment and partitioning, making sure tables are optimized for analytics. With this new capability, customers can streamline their end-to-end data pipeline, allowing them to continually feed fresh data into an Iceberg table without needing to build a custom data pipeline.

Real-time context to generative AI applications

Customers tell us how they want to gain insights from generative AI by being able to bring their data to large language models (LLMs). They want to bring data as it’s generated to pre-trained models for more accurate and up-to-date responses. Amazon MSK provides a blueprint that allows customers to combine the context from real-time data with the powerful LLMs on Amazon Bedrock to generate accurate, up-to-date AI responses without writing custom code. Developers can configure the blueprint to generate vector embeddings using Amazon Bedrock embedding models, then index those embeddings in Amazon OpenSearch Service for data captured and stored in MSK topics. Customers can also improve the efficiency of data retrieval using built-in support for data chunking techniques from LangChain, an open source library, supporting high-quality inputs for model ingestion.

More cost-effective and reliable stream processing

AWS offers the Kinesis Client Library (KCL), an open source library, that simplifies the development of stream processing applications with Kinesis Data Streams. With KCL 3.0, customers can reduce compute costs to process streaming data by up to 33% compared to previous KCL versions. KCL 3.0 introduces an enhanced load balancing algorithm that continuously monitors the resource utilization of the stream processing workers and automatically redistributes the load from over-utilized workers to underutilized workers. These changes also enhance scalability and the overall efficiency of processing large volumes of streaming data. We have also made improvements to our Amazon Managed Service for Apache Flink. We offer the latest Flink versions on Amazon Managed Service for Apache Flink for customers to benefit from the latest innovations. Customers can also upgrade their existing applications to use new Flink versions with a new in-place version upgrade feature. Amazon Managed Service for Apache Flink now offers per-second billing, so customers can run their Flink applications for a short period and only pay for what they use, down to the nearest second.

Conclusion

AWS has made new innovations in data streaming services, bringing compelling value to customers on performance, scalability, elasticity, and ease of use. These advancements empower businesses to use real-time data more effectively, which modernizes the way for the next generation of data-driven applications and analytics. It is still Day 1!


About the authors

Sai Maddali is a Senior Manager Product Management at AWS who leads the product team for Amazon MSK. He is passionate about understanding customer needs, and using technology to deliver services that empowers customers to build innovative applications. Besides work, he enjoys traveling, cooking, and running.

Bill Crew is a Senior Product Marketing Manager. He is the lead marketer for Streaming and Messaging Services at AWS. Including Amazon Managed Streaming for Apache Kafka (Amazon MSK), Amazon Managed Service for Apache Flink, Amazon Data Firehose, Amazon Kinesis Data Streams, Amazon Message Broker (Amazon MQ), Amazon Simple Queue Service (Amazon SQS), and Amazon Simple Notification Services (Amazon SNS). Besides work, he enjoys collecting vintage vinyl records.

[$] WP Engine granted preliminary injunction in WordPress case

Post Syndicated from jzb original https://lwn.net/Articles/1001783/

Since we last looked
at the WordPress
dispute
, WP Engine has sought
a preliminary injunction against Automattic and its founder Matt Mullenweg to
restore its access to WordPress.org, and more. The judge
in the case granted a preliminary injunction on December 10. The case
is, of course, of interest to users and developers working with
WordPress—but it may also have implications for other
open-source projects well beyond the WordPress community.

Disaster Recovery 101: Navigating Backup and Archive Infrastructure

Post Syndicated from Kari Rivas original https://www.backblaze.com/blog/disaster-recovery-101-navigating-backup-and-archive-infrastructure/

An illustration of a city scape with lines travelling up to a cloud representing digital transmission.

Aging infrastructure, strained budgets, and exponential data growth create unique challenges for disaster recovery (DR) planning. When assessing your backup and archive infrastructure, you’re probably balancing data governance, data sovereignty requirements, compliance requirements, and the needs of your end users. Many legacy data storage systems can create gaps in an otherwise airtight DR plan. 

Today, I’m talking through how to approach infrastructure decisions for your cyber resilience posture. You have a lot of options. On-premises? Cloud services? Hot? Warm? Cold? What combination works best for your needs? Understanding the nuances can help you sharpen your strategy.

Disaster recovery challenges

1. Relying on on-premises backup and archive infrastructure

Traditionally, businesses have relied heavily on on-premises backup solutions. Robust storage systems hold critical data, often backed up to secondary storage within the same physical location. While this approach offers a sense of control, it also presents vulnerabilities. 

On-premises backups are at risk of localized events like loss of power, fire, flooding, or other natural disasters. A geographically separate DR site or other far off-site backup is essential for complete protection and compliance. Without this, the organization risks losing critical data in cases of a regional outage or loss of access. 

The shift to public cloud and SaaS options opened the door to more secure and reliable data backup and disaster recovery solutions. By utilizing cloud-based storage and backup services, organizations can ensure that their data is protected in multiple locations, reducing the risk of data loss due to localized disasters. Additionally, cloud-based solutions offer scalability and flexibility, allowing organizations to easily expand their storage capacity as needed.

2. Falling into the replication trap

Many businesses have established alternate data centers as a secondary backup layer. However, these sites frequently only use replication technology. This situation can result in a scenario known as the “replication trap.” There is a risk that data compromised by malware is replicated to the DR site, leading to potential data loss. 

Off-site, immutable backups, independent of the primary site’s data, are a key component of a robust DR strategy. In cases of malware attacks or accidental data deletion by users, off-site immutable backups allow for data retrieval from a backup saved prior to the incident and reduce possible interruptions. 

3. Underestimating LTO limitations

Despite being viewed as a legacy technology, tape backups continue to be used in many organizations due to their reliability and cost-effectiveness. It is common to store tapes in a separate location to diversify data storage geographically, which helps reduce the impact of local disasters on data access and enhances overall data resilience. 

Off-site tape backups may increase recoverability but create challenges with recovery time objectives (RTO) because of the increased time it takes to retrieve data from a separate location and restore it using tape technology. Hardware issues can happen often and unexpectedly. Cloud-based data storage and archiving has gained popularity because of higher availability and cost savings over traditional tape backups. 

The cost and time required to operate multiple data centers and meet recovery times should also be considered in the requirements for your production and DR infrastructure. Never underestimate the risk to a successful recovery when facing time-consuming tasks like physical site recovery and data restoration from tape.

4. Leaving cloud-based productivity tools vulnerable

Cloud-based collaboration and communication tools like Google Drive and Microsoft 365 are commonly used by businesses and yet are often left vulnerable to data loss. Cloud services do not provide sufficient protection and recovery options that organizations likely need. 

Businesses often find that the responsibility for backing up this data falls on their own IT, as these services typically operate under a shared responsibility model that doesn’t offer comprehensive backup solutions. 

To ensure a reliable DR plan that includes cloud services, you should: 

  • Evaluate granular recovery requirements for productivity platforms like Google Workspace and Microsoft 365. 
  • Evaluate adherence to your long-term backup retention policy keeping in mind the regulations that your business might be subject to. 
  • Determine if data stored in cloud platforms needs to be backed up with immutability due to cyber insurance requirements or other security policies. 
  • Examine best practices for comprehensive, secure data protection for shared cloud drive services and SaaS productivity tools to address the lack of built-in recovery features.
  • Plan to store true backups of your SaaS data just as you would for any other data. It may seem redundant to back up cloud platforms to the public cloud, but doing so ensures that you have the right point-in-time backups you need and you can recover on your timeline—not Google or Microsoft’s. 

Cloud costs will need to factor into decisions for where to store your data. Cloud storage costs should be included as a non-functional requirement to make sure you can achieve your secure recovery goals without sacrificing affordability.

Best practices for cloud-based disaster recovery

Many enterprises rely on cloud-based DR solutions to ensure uninterrupted operations, protect critical data, and maintain customer trust. Unlike traditional DR methods, cloud-based solutions offer scalability, cost-effectiveness, and rapid recovery capabilities. To truly leverage the potential of these systems, it’s important to be aware of some key strategies and considerations to optimize your cloud-based disaster recovery plan, ensuring resilience in the face of unexpected disruptions.

  • Consider diversifying your cloud portfolio: Using the same cloud service provider for your backups as for your production data may not be necessary, as you don’t need the same level of performance for backup data. You could consider a tiered recovery approach based on the criticality of your applications and data.
  • Investigate existing tools for cloud compatibility: Many on-premises data protection tools like Synology or QNAP NAS devices also support cloud targets for backup storage. It’s important to match the capabilities of your current backup vendors to your recovery requirements and cloud storage budgets. 
  • Avoid paying for storage you’re not using: Carefully read the fine print when considering cloud storage costs. Hidden fees, minimum retention requirements, and complicated pricing tiers make accurate forecasting difficult and could leave you paying for unused storage just to reach certain discount tiers. 
  • Balance your budget with RTO and RPO targets: Using cloud data storage for production, backups, and archive can lead to some price shock as your environment scales. And moving data to lower cost storage tiers or cold storage may achieve attractive price reductions, but it often comes at the cost of recovery speed and added complexity. Look for a cloud storage provider with transparent pricing that makes it easier to plan your costs.

Finally, you should weigh your cloud-based options to evaluate platform compatibility, ongoing costs, and whether your CSP locks you in or out of specific ecosystems due to high storage costs, data transfer costs, and proprietary features. 

Leveraging cloud-based backup and archive infrastructure

Adopting cloud-based disaster recovery best practices is a key consideration for building a resilient and reliable business infrastructure. By developing a well-structured disaster recovery plan, determining the right mix of storage solutions, and optimizing costs with tiered recovery, businesses can minimize downtime and data loss during unexpected events. A proactive approach not only safeguards your organization’s operations but also strengthens customer trust and competitive advantage. In a world where disruptions are inevitable, being prepared is the key to bouncing back stronger and faster.

The post Disaster Recovery 101: Navigating Backup and Archive Infrastructure appeared first on Backblaze Blog | Cloud Storage & Cloud Backup

Security updates for Tuesday

Post Syndicated from corbet original https://lwn.net/Articles/1002496/

Security updates have been issued by Debian (gstreamer1.0), Fedora (jupyterlab and python-notebook), Oracle (gimp:2.8.22, gstreamer1-plugins-base, gstreamer1-plugins-good, kernel, php:8.2, postgresql, and python3.11), SUSE (aws-iam-authenticator, firefox, installation-images, kernel, libaom, libyuv, libsoup, libsoup2, python-aiohttp, socat, thunderbird, and vim), and Ubuntu (curl, Docker, imagemagick, and kernel).

Take Command of Your Career: Practicing Self-Advocacy as a Woman in Tech

Post Syndicated from Sam Keay original https://blog.rapid7.com/2024/12/17/take-command-of-your-career-practicing-self-advocacy-as-a-woman-in-tech/

Take Command of Your Career: Practicing Self-Advocacy as a Woman in Tech

As the year draws to a close, it’s essential—and often expected—to reflect on our achievements and lessons learned in preparation for annual performance reviews and setting future goals.For women in tech, this reflection period can be an especially powerful tool. The industry often demands that women work harder to prove their worth in spaces where their contributions are sometimes overlooked or undervalued. Performance reviews and goal-setting moments are opportunities to take command of your career, highlight your contributions, and advocate for your worth.

Many women, particularly those in male-dominated fields like tech, have been conditioned to prioritize modesty over self-promotion. This can make self-advocacy feel uncomfortable, even though it is essential for career growth. As a result, performance reviews often provoke anxiety instead of empowerment. It’s common for women to downplay their achievements or struggle to articulate their value in a way that feels authentic.Shifting this narrative is critical. Self-advocacy isn’t about bragging; it’s about ensuring that your contributions are recognized and valued in spaces where they might otherwise be overlooked.

Why Self-Advocacy Matters for Women in Tech

In male-dominated industries, women often face additional challenges, such as biases around competence, communication styles, and leadership potential. Self-advocacy helps combat these challenges by ensuring your contributions are visible and your goals are clear. Advocating for yourself helps you recognize your value and push back against imposter syndrome—a common experience for women in underrepresented spaces.

When you embrace self-advocacy, you empower yourself to ask for the opportunities, recognition, and compensation you deserve. But how can you self-advocate in a way that feels authentic and impactful? Here are some strategies that have helped me navigate and excel in self-advocacy while working in tech.

Keep a Hype Document

When preparing for a review or manager conversation, it’s easy to forget big wins from the past 6-12 months, making the process feel daunting.

To stay on top of this, I keep a ‘Hype Document’ that I update monthly. I track every positive contribution—big or small—with notes on its impact, alignment to goals, and connection to Rapid7’s core values. This document becomes my go-to for 1:1s, reviews, and team discussions, ensuring I always have relevant wins ready to share.

It’s also a great confidence booster when imposter syndrome creeps in, reminding me of my progress and value. At year-end reviews, it turns what could feel overwhelming into an empowering opportunity to demonstrate my impact with clear, compelling evidence.

Make the most of 1:1s

Weekly or bi-weekly 1:1s are a great opportunity to steer conversations with your manager. When employees take the lead, it shows they’re managing their responsibilities effectively, builds trust, and helps managers assess readiness for growth opportunities.

I apply the same approach with my own boss—using 1:1s to provide updates, seek guidance, and demonstrate my readiness for new challenges, which supports my career advancement.

Prepare ahead by setting an agenda, highlighting recent wins, and sharing the impact of your work. Even the best managers can’t see everything, so use this time to ensure your contributions are recognized and identify areas for growth or improvement.

Map out your goals

In order to know how and when to advocate for yourself, you need to have a clear direction of what your desired outcome is. Define your career aspirations clearly, whether it’s leadership, technical expertise, or a shift in focus. This clarity helps you communicate your vision to others and align their support.

Share your expectations

Your manager can’t help you meet goals they don’t know about. Use your voice to ask for what you want, whether it’s a salary increase, leadership role, or new focus area.

Be clear and transparent about your aspirations. This is your career, not a hobby—take ownership and communicate your expectations confidently. Your manager can provide feedback, identify skill gaps, and outline next steps to help you move forward.

Remember, your manager should be your second-biggest advocate—you must be your first.

Nail your elevator pitch

In tech, roles and contributions can be highly technical, making it harder to summarize your value. Crafting a strong elevator pitch helps you translate your contributions into relatable, impactful terms.

For example, instead of saying, “I manage the Proposal team,” try:
“I manage a global team of accredited Proposal Managers. We drive tens of millions of dollars in revenue annually by winning bids and ensuring smooth contract processes.”

Grow your network and seek mentorship

Nobody achieves a great career all on their own. Networking—whether internal, external, or through mentorship—sets you up for success.

At Rapid7, I’ve used our InsightCoffee program to connect with colleagues across teams. These conversations have opened doors to collaboration, deepened my understanding of the business, and given me opportunities to share my goals and practice my elevator pitch.

Many organizations also have internal chats and channels for communication. Put yourself out there—share information, offer help, and build connections. People remember those who teach them something or lend a hand in tough moments, so look for opportunities to add value.

Mentorship is another way to grow your network and address skills gaps. This could mean finding a mentor or offering to mentor someone else. My mentor relationships have been invaluable as sounding boards for feedback and advice.

Efforts like these increase your visibility and grow your network, which are key to leadership and enhancing your personal brand.

Solicit (and give!) Feedback

Like many tech companies, Rapid7 uses a 360-feedback tool to help employees identify strengths and areas for growth. Using this tool regularly can feel intimidating, especially when requesting constructive feedback, but keeping an open mind allows you to unlock its value as a resource for long-term success.

Providing feedback is just as important. It’s a chance to celebrate others’ achievements, strengthen relationships, and connect around shared goals. Embracing feedback—both giving and receiving—helps you build stronger connections and demonstrate the impact of your work.

Wrapping Up

If I were to summarize the main takeaways from self-advocacy, it comes down to this:

Believe you deserve it, and shamelessly ask for it.

Start small when implementing these practices. Share a few wins in your 1:1s, ask your manager what they consider noteworthy, or spend time networking to discuss your goals and challenges. You could also share a big win in a team meeting or ask others how they approach self-advocacy. It’s not a dirty word—it’s about recognizing your value and earning the recognition you deserve to advance your career.

While self-advocacy may feel uncomfortable at first, the more you practice, the more natural it becomes. Growth happens outside your comfort zone—you deserve it, and you can do it!

What’s more, every step you take to advocate for yourself inspires others, raising your profile while fostering a culture of growth and fulfillment. As the saying goes, ‘a candle loses nothing by lighting another candle’.

To learn more about the culture at Rapid7, our Rapid7 Women’s community, and other resources, visit our careers page.

Five reasons to join the Astro Pi Challenge, backed by our impact report

Post Syndicated from Vicky Fisher original https://www.raspberrypi.org/blog/five-reasons-to-join-the-astro-pi-challenge/

We are excited to share our report on the impact of the 2023/24 Astro Pi Challenge. Earlier this year we conducted surveys and focus groups with mentors who took part in the Astro Pi Challenge, to understand the value and impact the challenge offers to young people and mentors. You can read the full report here, but here are the highlights.

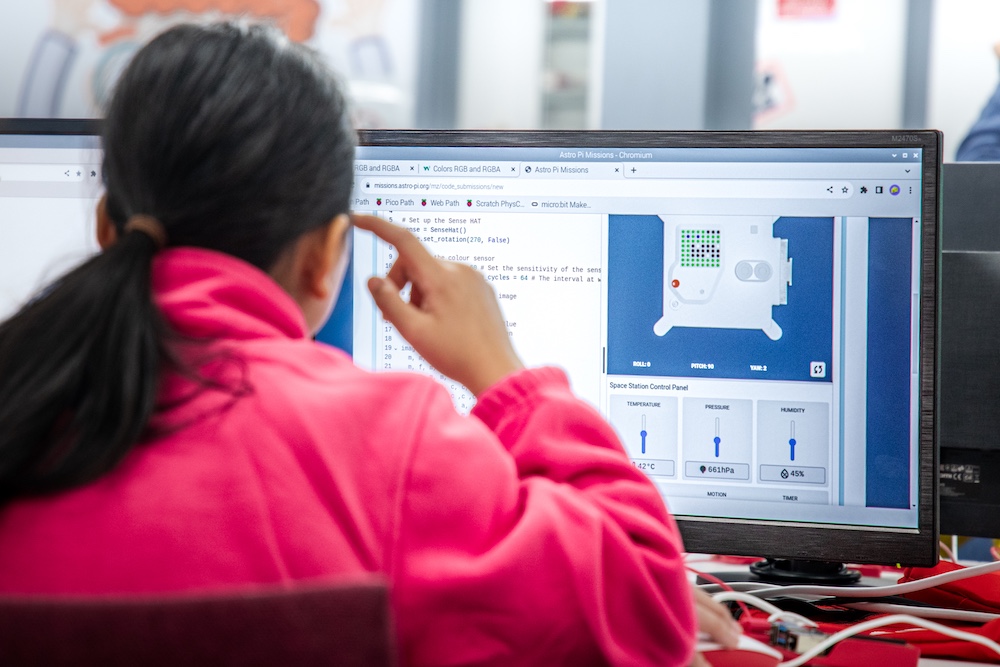
A child taking part in Astro Pi Mission Zero.

What is the Astro Pi Challenge?

The European Astro Pi Challenge is an ESA Education project run in collaboration with the Raspberry Pi Foundation. It offers young people the amazing opportunity to learn how to code and conduct scientific investigations in space, by writing computer programs that run on Raspberry Pi computers on board the International Space Station (ISS). The annual Astro Pi Challenge is open to young people up to age 19 in ESA member and associate countries.

Each year, there are two missions: Mission Zero and Mission Space Lab.

Five reasons to take part in the Astro Pi Challenge

Based on the findings in this report, we wanted to highlight five great reasons to take part in the Astro Pi Challenge, and direct you to some resources to help you get started — there is still plenty of time to enter the 2024/25 challenge!

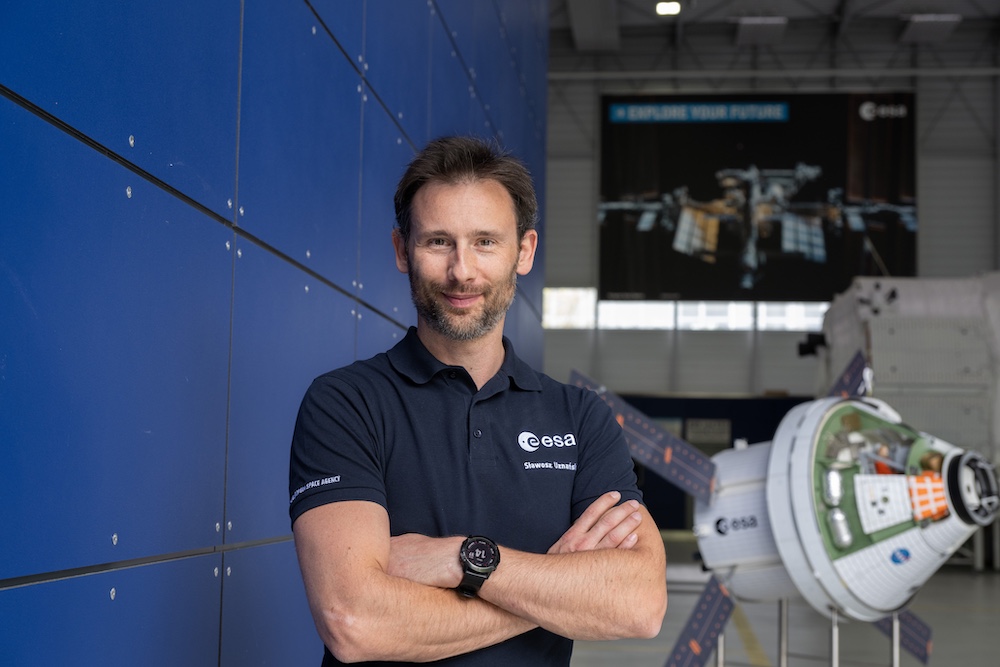
ESA astronaut Sławosz Uznański Astro Pi Challenge 2025 ambassador.

1. Young people get to run their code in space

Mentors told us how excited young people were to be working on something that connected with the real world, and how proud they were that their code ran on the International Space Station.

“Participating in Mission Space Labs offers students a great opportunity to work with the International Space Station, to see the Earth from above, to challenge them to overcome the terrestrial limits.” – Mission Space Lab mentor

2. Young people are inspired to continue to learn

91% of mentors told us that young people who successfully wrote code for Mission Space Lab were likely or very likely to participate in computing and digital making challenges in the future.

Mission Zero mentors shared that young people who saw others take part in the mission were inspired to get involved.

3. Young people learn new skills

Mission Space Lab mentors told us that young people who successfully wrote code for Mission Space Lab had a greater understanding of STEM concepts, and increased their skills and confidence in computing and digital making.

Mentors also said that Mission Zero provides a great first step into using Python.

“I think it was very good at setting up the first bit of Python and just having a very limited command set and a very quick result…” – Mission Zero mentor

4. Astro Pi mentors have fun

It’s not just the young people that enjoy Astro Pi — 95% of Mission Space Lab mentors and 99% of Mission Zero mentors said they somewhat or very much enjoyed taking part.

5. We provide the resources and support Astro Pi mentors need

Mentors gave us positive feedback on the guidance we provided to help them support young people. This year, we have produced even more resources and ways to support mentors to lead missions.

“The Mission [Space] Lab guide was fantastic for my students; step by step” – Mission Space Lab mentor

How to get involved

Astro Pi opened for registration on 16 September this year, and there is still plenty of time for you to sign up and run the missions with your young people. You can find all the information you need to take part on astro-pi.org, including the mentor guides, which help you prepare to run the activities.

Mission Zero mentor guide
Mission Space Lab mentor guide

We also provide project guides for Mission Zero and Mission Space Lab that walk young people through the steps they need to follow to get a working program ready for submission.

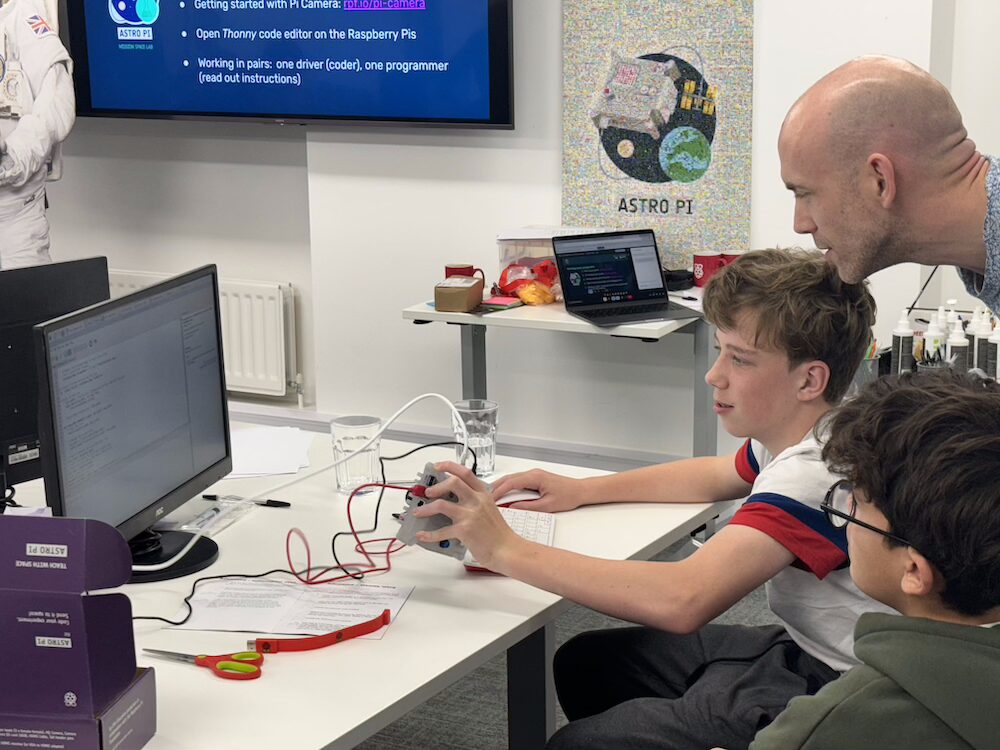
Mission Space Lab workshop held at RPF HQ.

If you would like some help getting started, you can:

Key dates

17:30 – 18:30 CET, 16 January – Mission Space Lab livestream and technical Q&A
17:30 – 18:30 CET, 28 January – Mission Zero codealong
09:00 CET, 24 February – Mission Space Lab closes
09:00 CET, 24 March – Mission Zero closes

The post Five reasons to join the Astro Pi Challenge, backed by our impact report appeared first on Raspberry Pi Foundation.

„Той е моя вяра, мой свят, болест моя, лекар мой.“ Хомосексуалност и ислям (продължение)

Post Syndicated from Атанас Шиников original https://www.toest.bg/toy-e-moya-vyara-moy-svyat-bolest-moya-lekar-moy-homoseksualnost-i-islyam-produlzhenie/

<< Към първа част

… И все пак каква е историческата гледна точка към хомосексуалните практики в мюсюлманския свещен закон?

„Той е моя вяра, мой свят, болест моя, лекар мой.“ Хомосексуалност и ислям (продължение)

Сложна, но не безкрайно противоречива, ако предприема логически непоследователния ход на представяне на извод преди аргумента. Впрочем понятие като „хомосексуалност“ не съществува в мюсюлманската традиция. Основният термин е лиуат, а пък за онзи, който го практикува, се изработва понятието лути, оттук и глаголът талаууата, тоест „постъпвам като народа на Лут“. Те имат корени в текста на Корана, където се говори за греха на „народа на Лут“ и последвалото му унищожение. 

Лут е кораничният еквивалент на библейската фигура на Лот от разказа за Содом и Гомор в Битие 19 в Библията. В мюсюлманското Свещено писание се появява на няколко места, например 7:80, където се говори за народа на Лут и „скверността [фахиша], която преди вас не е сторвал никой народ“. Въпросната „скверност“ откриваме и в 27:54 или пък в 29:28. Без изрично да се указва от какъв характер е, историческата правна и богословска традиция недвусмислено развива възгледа, че става въпрос за практикуване на содомия между мъже. Кораничният разказ задава и тона на предписаното наказание за прегрешението, доколкото именно „ураган от камъни“ (54:34) и „порой камъни от глина“ (15:74) е средството, чрез което Аллах наказва народа на Лут.

Сборниците с преданията на Пророка, т.нар. Сунна, като друг основен източник на правно нормотворчество, също обрисуват практиката със силно негативни краски. Там „народът на Лут“ се появява сред заръките на Пророка в тематичните раздели, посветени на онази особена категория наказания, обозначавани с термина хадд, букв. „граница“ – познатите ни отрязвания на ръката на крадеца, пребиване с камъни за прелюбодейство, екзекуция при метеж срещу управника и пр. Достатъчно красноречиви са опасенията на Пророка: „… нещото, от което най-много се страхувам за общността ми, са делата на народа на Лут.“ Относно прегрешилите пък той заръчва:

… убийте с камъни онзи, който е отгоре, както и онзи, който е отдолу, както онзи, който го върши, така и онзи, комуто го вършат. 

А както знаем, поне от времето на прадядото на мюсюлманската юриспруденция Аш-Шафии от VIII–IX век, основните стълбове на мюсюлманското право са Корана и Сунната. От тях чрез техники като аналогията (кийас) и консенсуса на богословите (иджма‘) се извличат приложими в различни контексти постановки. На този принцип и до днес се конструират и отговорите на богословите и правистите в големите портали за онлайн консултации (фатауа). И тук се случва нещо подобно – чрез аналогия с прегрешението на прелюбодеянието (зина), тоест сексуални отношения извън легитимната рамка на брака или с робини, хомосексуалната практика се разглежда като подлежаща на същото наказание. И то традиционно е пребиване с камъни. По силата на предадени истории около зетя на Пророка Али ибн Аби Талиб и неговия близък съратник и пръв халиф Абу Бакр се допуска и изгаряне или хвърляне от високо. 

Аналогията между прелюбодеянието и хомосексуалния акт е стандартна. Големите мюсюлмански правни школи се придържат основно към нея, при все че съществуват известни нюанси – за някои течения смъртно наказание се полага при всички случаи, други въвеждат разграничаване в зависимост от това дали извършителите са женени, или не. И накрая идват тези, според които наказанието може да бъде смекчено. Вместо санкция от категорията хадд, която не подлежи на оспорване, се предписва наказание като бой с камшик от по-меката категория та‘зир, тоест по преценка на шариатския съдия (кади). Така смята например Ибн Хазм от Кордоба през XI век. А той, въпреки че принадлежи към една от най-буквалистичните школи в мюсюлманското право, си позволява доста фриволни асоциация по темата за любовта между мъжете в най-известното си литературно съчинение с поетичното заглавие „Пръстенът на гълъбицата“. 

По смисъла на така зададената терминологична и нормативна рамка, предмет на регулация са хомосексуалните отношения между мъже, но най-вече самият акт на съвкупление. И те винаги се разглеждат в силно негативна светлина. Отношенията между жени рядко стават предмет на анализ и също касаят самия акт, който бива обозначен с друг термин – сихак или мусахака. Той, подобно на лиуат, впоследствие придобива и по-общо значение и започва да се употребява в смисъла на лесбийство. 

Но как гледат днешните богослови на постъпилите към тях запитвания от мюсюлмани?

Какво е наказанието за хомосексуалност [лиуат] и има ли разлика между онзи, който го върши, и комуто го вършат? –

задава въпроса си един мюсюлманин в портала на влиятелния богослов Мухаммад Салих ал-Мунаджжид,

Подобен тип запитвания и отговорите им са златна мина. Тук отговорът на шейха е подробен, затова започва с кратко резюме. Ако искате, четете само резюмето, както при османските мюфтии, които отговарят единствено с „Да, може“ или „Не, не може“, без да са длъжни да се обясняват. 

Резюмето е кратко и недвусмислено – всички авторитетни съратници на Пророка, твърди богословът, са напълно съгласни, че извършителят трябва да бъде убит. Само че, казва, мненията им се различават по начина на екзекуцията. Някои, измежду които е и Абу Бакр, верният приятел на Пророка, твърдят, че престъпникът трябва да бъде изгорен с огън. Други пък препоръчват, че трябва да бъде хвърлен от високо, а пък трети – че трябва да бъде убит чрез замеряне с камъни. 

Но след времето на Пророка правистите развиват по-детайлни мнения. Някои казват, че при всички случаи трябва да бъде убит, независимо дали е женен, или не, а според други, ако е женен и го извърши, подлежи на убиване с камъни, иначе само го бичуват. Подробният отговор пък се опира до голяма степен на разсъждението на богослова Ибн Кайим ал-Джаузия от XIV век. 

Съществува обаче казус, при който не са те хванали, така че е възможно да не изпиташ цялата строгост на шариата. За такъв случай разбираме от портала, финансиран от катарското Министерство на религиозните дела, където има цял раздел за наказания, свързани с хомосексуалност (лиуат) и „извращение“ (шузуз, един от другите термини).

Именно там мюсюлманин на 27-годишна възраст споделя, че бил изкушен многократно от хомосексуалността, за което се разкайва, и пита какво да стори. Отговорът е очакван: препоръчва се покаяние според редица предания от Пророка и Корана, като отново се цитира съчинението на Ибн Кайим ал-Джаузия. Някои текстове се превръщат в евъргрийн и си остават такива дори след седем столетия. Очертават се обаче и трите степени на подхлъзване към този грях (и престъпление, доколкото по шариата често пъти категориите се припокриват). Първата е само чрез гледане, втората е чрез телесен контакт под формата на прегръдки и други интимности, и накрая, третата е самият акт, който е най-голямата скверност.

Сексуалните практики между жени също не остават встрани от запитванията на мюсюлманите. Ето какво гласи друг въпрос:

Знам, че практикуването на секс между жени е възбранено, но искам да знам какво е наказанието. Сестра във вярата ми каза, че наказанието е точно като това за прелюбодеянието – бой с камшик за неомъжените и пребиване с камъни за омъжените.

Отговорът на шейх Мунаджжид е нюансиран – при все че някои религиозни учени го смятат за голям грях, не се полага наказание като за прелюбодеяние, защото не е такова. Полага се възпитателна наказателна мярка по преценка на съдията. Богословът Ибн Кудама също намира място в отговора – според него Пророкът е казал, че сексуалният контакт между жени все пак се смята за прелюбодейство (зина), но не се полага пълното наказание, защото няма как да се осъществи акт на проникване (джима‘). Оттук и следва отсъждането на наказание по преценка на съдията. Дават се и препоръки за излекуване от порока: обръщане към Аллах в чистота, преклонение и благочестие, свеждане на погледа с цел избягване на изкушенията, спомен за починалите, на които е отсъдено според делата им и не могат да направят нищо, за да изкупят греховете си, или да добавят още добри дела, занимания с полезни неща, а накрая нещо съвсем прагматично – препоръка за женитба колкото може по-скоро. 

Този текст няма претенция за всеобхватност. Със сигурност не отчита цялата палитра от нюанси в отношенията между половете. Не разглежда например възгледите за трансджендър хората, за хора с белези на двата пола или за кросдресинга. Не проблематизира в дълбочина правата на ЛГБТ общностите в Близкия и Средния изток. Няма и за цел да сравнява през границите на традициите в други монотеистични религии, нито пък да търси паралели с античния идеал за любовта между зрял мъж и младеж. За сметка на това открехва пролука, през която да надзърнем към обосновката на точно определено устойчиво отношение към ЛГБТ общността. С него може да сме съгласни или не, но то със сигурност съществува. 

Може да твърдим, подобно на изследователката, цитирана в началото, че тази строгост произтича не от „задълбочено разбиране“ на религиозния закон, а от изначално предпоставена и аксиоматично зададена цисджендър гледна точка. Звучи ми като изказване в духа на „те не са разбрали правилно Корана и Пророка и са си измислил фундаментализми“. Не бих се наел с такъв дързък мисловен експеримент чрез омаловажаване на значението на нормативния текст. Не може да си затворим очите за основанията за такова отношение към практиките на гей общността. 

Но какво можем да направим тогава? Трябва да се „считаме с реалностите“, както казва Тодор Живков в една от речите си.

ЛГБТ общности в Близкия и Средния изток са съществували и ще съществуват независимо от възгледите на „ходжите“,

както пейоративно ги наричат раздразнените им противници.

Може да се опитаме например да разделим постановките на свещения закон от тези на вярата в духа на едно „осветскостяване“ на религията, подобно на историческите процеси на секуларизация в Европа. Според това виждане придържането към свещения закон е историческа отживелица, следователно е незадължително. Коранът не е наръчник по право, твърдят застъпниците на такъв възглед. Оттук и религиозният закон може бъде категорично поставен настрани от основните положения на вярата като несъществен. 

Може да се предприеме и друг ход. Да се опитаме да обосновем иновативни тълкувания – както при съвременните усилия да се предоговорят понятията за пол в исляма по линия на изпълване на думи като фитра (сходно на „природа“) с ново съдържание, включващо и това да си гей. По редица причини тези контранаративни начинания в посока разчупване на основни доктринални положения засега остават в сферата на екзотичната интелектуална спекулация. И в момента, в който нормата започне да определя практиката, крайният резултат – с цялата му строгост – може да бъде доста предсказуем. Без значение дали ни харесва, или не.

Наказанието на народа на Лут, ръкопис от XVI век на „Житията на пророците“ от Исхак ибн Ибрахим ан-Нишапури (XII век), дигитална колекция на Берлинската библиотека

В рубриката „Ориент кафе“ Атанас Шиников поднася любопитни теми, свързани не толкова с горещата политика, колкото с историята и културата на Близкия изток. А той, древен и днешен, е по-близко до нас и съвремието ни, отколкото си представяме.

Announcing systemd v257

Post Syndicated from Lennart Poettering original https://0pointer.net/blog/announcing-systemd-v257.html

Last week we released systemd v257 into the wild.

In the weeks leading up to this release (and the week after) I have
posted a series of serieses of posts to Mastodon about key new
features in this release, under the
#systemd257 hash tag. In
case you aren’t using Mastodon, but would like to read up, here’s a
list of all 37 posts:

I intend to do a similar series of serieses of posts for the next systemd
release (v258), hence if you haven’t left tech Twitter for Mastodon yet, now is
the opportunity.

A sapling matures: meet sq 1.0

Post Syndicated from jzb original https://lwn.net/Articles/1002411/

The Sequoia PGP project has announced
version 1.0 of the sq command-line tool for managing OpenPGP
encryption and signatures. It also provides a decentralized public
key infrastructure
(PKI), and key management facilities. This is
the first stable release since development began on the project in
2017.

sq‘s PKI is probably its most notable feature, and the one we invested
the most time in. The PKI is used to authenticate certificates, and
messages. Authentication is necessary to ensure that you are
encrypting to the person you think you are, and to identify who really
authored a message; without authentication, encryption and
verification are much weaker.

The collective thoughts of the interwebz