Post Syndicated from Explosm.net original https://explosm.net/comics/judge-a-book
New Cyanide and Happiness Comic
Post Syndicated from Explosm.net original https://explosm.net/comics/judge-a-book
New Cyanide and Happiness Comic
Post Syndicated from xkcd.com original https://xkcd.com/3231/
Post Syndicated from Let's Encrypt original https://letsencrypt.org/2026/04/10/test-sites.html
Have you ever needed to make sure your website has a broken certificate? While many tools exist to help run an HTTPS server with valid certificates, there aren’t tools to make sure your certificate is revoked or expired. This is not a problem most people have. Tools to help manage certificates are always focused on avoiding those problems, not creating them.
Let’s Encrypt is a Certificate Authority, and so we have unusual problems we need to solve.
One of the requirements for publicly trusted Certificate Authorities is to host websites with test certificates, some of which need to be revoked or expired. This gets messed up more than you might expect, but it’s a bit tricky to get right. Test certificate sites exist to allow developers to test their clients, so it’s important that they’re done right.
We’d previously used certbot, nginx, and some shell scripts, but the shell scripts were getting a bit too complicated. So we wrote a Go program tailored to the specific needs of a CA’s test certs site.
We need to host three sites per root certificate:
Valid is easy enough; it’s the normal case of any other website. This is a solved problem.
Expired, too, is pretty easy. Issue one certificate, wait until it expires, and then you can use it forever. Not a normal feature, but so long as your webserver doesn’t get upset at it being expired, it’s easy to set up once and leave it.
Revoked, though, is where it’s easiest to slip up. You could fail to revoke a certificate and serve a perfectly valid one, or you could let your revoked certificate expire. Making sure your website is serving a non-expired but revoked certificate is not something any of the off-the-shelf tools support.
In order to implement our program, we need a few different ingredients to mix together.
First and foremost, we need to be able to get certificates. Because we’re writing this in Go, we’re using Lego as a library to request the certificates. Obtaining a certificate requires completing a domain validation challenge. We can hook Lego up to the Go webserver we’re using to complete TLS-ALPN-01 validation. We use that challenge type because it doesn’t require any more setup beyond exposing our webserver to the internet.
To get a revoked certificate, we request a certificate and then revoke it. That’s something we can do with Lego and ACME too: The account which issued a certificate can request it be revoked. We then need a way to check that the certificate is revoked. Certificates contain an HTTP URL pointing to the Certificate Revocation List (CRL) which we poll until our certificate’s serial number appears in it.
Let’s Encrypt implements the ACME standard, which defines how clients can get certificates. In general, we think ACME clients integrated into webservers are often the best way to get certificates for websites. They can automatically handle challenges, managing and reloading certificates, and overall minimizing the amount of work and reducing problems.
We also need a way to wait until a certificate is in the right state. The valid certificate is ready to use right away, but that’s not true for the revoked and expired certificates. The revoked certificate needs to wait at least until it appears in a CRL, which can be up to an hour. Expired certificates need to wait even longer: Even if we request the shortest-lived certificates we offer, that’s still six days. To handle this, our program stores a “next” certificate instead of immediately overwriting the current one. We wait at least 24 hours for the revoked certificate to make sure any CRL caches or push-based CRL infrastructure have time to process the revocation. The expired certificate has to wait until it passes its expiration date. After the program decides a certificate is ready, it replaces the current certificate and passes it off to the webserver. Normal ACME tools don’t support this because they can usually start using a certificate as soon as it’s obtained.
And finally, we need a webserver to host the certificates. We’re using Go, which has a great built-in TLS and HTTP serving stack we can use. The Go TLS server takes a GetCertificate callback function that decides what certificate to use for each new connection. We have all our certificates in-memory and select the right one to serve based on the request’s SNI. This function is also where we hook up Lego to serve the challenge certificates required for TLS-ALPN-01. Because we prioritize serving the correct certificate over uptime, we refuse to handle a connection if the corresponding certificate is expired (unless it should be expired!).
If you visit one of our revoked sites, you might not get an error message. Revocation checking in browsers varies pretty widely, and has historically not worked great. Today’s state-of-the-art is Firefox’s CRLite, which is efficient and reliable. Ubuntu is deploying the same technology in their upki project. We hope other browsers and operating systems follow suit. The upki project is a great example of a project making use of these revoked test certificates, too.
The actual content of the website isn’t terribly important: We just have a little HTML page explaining what the site is. But since this website is meant for testing clients, there’s more than just browsers connecting. In particular, it’s pretty routine that I try connecting with curl or some other terminal http client, and getting a bunch of HTML spewed to your terminal isn’t very nice.
As a small easter egg, we added a plain text version of the website with an ASCII art version of our logo that we serve if your HTTP client doesn’t include text/html in its Accept HTTP header. You can pass a ?txt or ?html URL parameter to specifically request one or the other version of the content, if you just want to see the ASCII art.
Let’s Encrypt has four root certificates right now. Each of them have test sites linked both here and from our documentation.
| Root X1 | valid | expired | revoked |
| Root X2 | valid | expired | revoked |
| Root YE | valid | expired | revoked |
| Root YR | valid | expired | revoked |
As with a lot of Let’s Encrypt, the code for this project is open-source. You can find it at https://github.com/letsencrypt/test-certs-site/. Other Certificate Authorities who need to run similar test certificate sites are welcome to use it. If you need any features that would make using our test certs site easier for your TLS/HTTPS client testing, please feel free to create an issue on that repository.
Post Syndicated from Ryan Smith original https://www.servethehome.com/dell-pro-rugged-12-tablet-review-the-resilient-road-warrior/
Today we are taking a look at something a little different for ServeTheHome with Dell’s Pro Rugged 12 Tablet. The flagship model of Dell’s ruggedized hardware lineup, Dell’s toughly-armored tablet is aimed at the most extreme segment of road warriors: namely, those who need a Windows tablet or 2-in-1 that can stand up to brutal […]
The post Dell Pro Rugged 12 Tablet Review The Resilient Road Warrior appeared first on ServeTheHome.
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/IBsbyjpi-Hw
Post Syndicated from Douglas McKee, Director, Vulnerability Intelligence original https://www.rapid7.com/blog/post/ai-what-project-glasswing-means-for-security-leaders
Anthropic’s Project Glasswing matters because it offers an early look at how quickly software flaws may soon be found, validated, and potentially turned into viable attack paths, even if that capability is currently limited to a closed partner program. Anthropic says its restricted Claude Mythos Preview model has already identified thousands of high-severity vulnerabilities, including flaws in major operating systems and browsers, and in some cases developed related exploits autonomously.
Some early coverage has emphasized the risks and need for restraint in deploying capabilities like this, and for most organizations, it won’t immediately change day-to-day security operations. What it does offer is a signal of where the industry may be heading: a future where discovery moves faster, and where the pressure shifts to everything that follows, including prioritization, remediation, validation, and response. Glasswing feels less like the storm itself and more like the first sign that the radar is getting better faster than the emergency plan. How well can we handle what comes next?
Project Glasswing is Anthropic’s new defensive security initiative built around Claude Mythos Preview, a model the company is not releasing publicly because of its cyber capabilities. Anthropic says the preview is being provided to a limited set of organizations, including AWS, Apple, Broadcom, Cisco, CrowdStrike, Google, JPMorganChase, the Linux Foundation, Microsoft, Nvidia, and Palo Alto Networks, with access also extended to more than 40 additional organizations. Anthropic has also committed up to $100 million in usage credits and additional support for open-source security work.
That makes this more than another AI feature release. Anthropic is effectively signaling two things at once. First, there is a meaningful backlog of serious, undisclosed vulnerabilities still out there. Second, capabilities like this are sensitive enough that broad public release would be irresponsible right now. For security leaders, the message is not that AI replaces human researchers. It is that AI is becoming materially more useful in vulnerability research, and defenders should be thinking now about how they will handle what comes next.
It would be easy to read this as a story about faster vulnerability discovery alone. That misses the more important point. If Anthropic’s claims are directionally right, the immediate pressure does not land on discovery alone. It lands on everything downstream of discovery: asset context, exploitability analysis, ownership, compensating controls, patching, exception handling, validation, and detection coverage. In other words, the harder part of security becomes more obvious.
That matters because most enterprise programs do not struggle to generate findings. They struggle to decide which findings matter first, who should act, what can wait, and whether remediation actually reduced exposure. If AI pushes vulnerability discovery into a new gear, weak operating models will feel that pressure first. Backlogs get bigger. Teams drown in queues. Fix rates do not keep pace. Risk stays put. That is not a model problem. It is an execution problem.
This is why security leaders should be careful with the framing. The headline is not “AI found bugs, therefore security improves.” The headline is that the bottleneck may be moving downstream even faster than expected. That raises the value of programs that connect exposure management, remediation, and runtime defense instead of treating them as separate activities.
Some of the reported examples are striking. Anthropic and media reports say Mythos Preview found a 27-year-old OpenBSD vulnerability, a 16-year-old FFmpeg flaw that reportedly evaded millions of automated test executions, and multiple Linux kernel vulnerabilities that could be chained together. Anthropic has also said the model reproduced vulnerabilities and built proof-of-concept exploits at a high success rate in testing. Even if individual examples get debated over time, the pattern is the important part. The model appears to compress several human steps into one workflow, from discovery to validation to exploit construction.
Security has seen faster discovery before. Fuzzing changed the game. Better automation changed the game. Large-scale bug bounty operations changed the game. What is different here is the combination of reasoning, coding, persistence, and iteration inside a single model loop. If that loop becomes reliable, then defender workflows built for human-speed intake and triage will come under more strain. That does not make coordinated disclosure obsolete. It makes today’s processes look slow.
CISOs do not need to decide this week whether Anthropic’s model changes the entire market. They do need to ask a more practical question: if my environment starts surfacing materially more vulnerabilities tomorrow, what happens next?
For many organizations, that answer is uncomfortable. Findings land in multiple tools. Asset inventory is incomplete. Internet exposure is only partly understood. Ownership is fragmented. Patch cycles are slow. Exceptions pile up. Security teams cannot easily prove that a fix changed reachable risk in the real environment.
That is where this news becomes relevant. AI-driven discovery does not reduce the need for an exposure-led security model. It increases it. The organizations that benefit most will not be the ones with the biggest pile of findings. They will be the ones that can connect those findings to business-critical assets, internet exposure, identity paths, existing detections, remediation workflows, and validation.
A good board-level translation is that faster discovery only has value if the organization can prioritize effectively, remediate quickly, and prove that the fix reduced real exposure. Otherwise, the result is more volume and more noise.
For engineers, this announcement is less a reason to either celebrate or dismiss the technology than it is a sign that defensive research workflows may change quickly if capabilities like this spread more broadly. Today, Glasswing is still limited to a small group of trusted partners, so this is not yet a shift most engineering teams will feel directly in their daily work. What it does offer is an early look at where software security may be heading.
AI-assisted discovery is likely to become more common across secure development, code review, infrastructure testing, and open-source maintenance. That creates real opportunities. Models can help explore deep code paths faster, challenge assumptions earlier, improve reproduction, and generate more detailed reports than many conventional workflows produce today.
The harder question is what comes next. If AI can generate more findings and more exploit hypotheses, engineering teams will need stronger intake, validation, and prioritization discipline, not less. Triage quality, deduplication, severity context, reproducibility, and ownership all become more important as discovery speeds up. Many maintainers and internal product security teams already struggle with volume, and machine-generated reporting could make that problem worse if workflows do not mature alongside the tooling.
At the same time, that is only one side of the equation. If models can help find bugs faster, they may also help defenders confirm impact, suggest code changes, support patch development, and reduce some of the manual effort that slows remediation today. In the longer run, the same AI shift that increases pressure on defenders may also help them absorb some of that pressure. The real issue is not whether AI adds more findings. It is whether teams can use it to shorten the full path from discovery to decision to verified fix.
The best engineering response, then, is not to argue about whether these models are impressive. It is to improve the operating path around them. Can the team confirm impact quickly, tie a flaw to reachable attack surface, deploy a patch or control change, and verify that exposure is actually reduced in production? If that chain does not improve, faster discovery alone will not deliver much value.
Anthropic’s decision to restrict access is understandable, but it also underscores a harder truth – capabilities like this rarely stay contained for long. Whether through competitors, open customization, or less restrained releases, the broader industry should assume similar models will become more widely available in the near term. For most organizations, this is not a market-wide operational shift today. It is a warning of what may be closer than it appears.
That signal arrives at a time when many security operations teams are already under strain. Most can investigate only a fraction of the alerts and exposures their environments generate, which keeps them in reactive mode, manually triaging high-priority signals across fragmented telemetry while scale and consistency remain difficult to achieve. Many promises of AI super-productivity have not yet translated into day-to-day operational relief. That is part of what makes Glasswing worth paying attention to. It points to a future where discovery may improve faster than most response models do.
It also points to an opportunity. If AI can compress parts of vulnerability research, the same broader class of capabilities may eventually help defenders improve prioritization, investigation, remediation, and validation as well. That is where the next phase of security is likely to be decided. Not in whether organizations can generate more findings, but in whether they can use AI to make response workflows faster, more consistent, and more precise.
From our perspective, that raises the operational bar for defenders. If discovery gets faster, organizations will need to shorten time to detect, accelerate time to patch, and manage vulnerability backlogs with far more urgency than they do today. That starts with a threat-led view of the environment. Teams need to understand which weaknesses are most exposed, most exploitable, and most likely to matter in real attack paths so they can prioritize action based on actual risk, not just queue depth.
That is the practical lesson from Glasswing. It feels less like the storm itself and more like the first sign that the radar is getting better faster than the emergency plan. For most organizations, the announcement does not change the queue tomorrow morning. What it does change is the urgency of preparing for a future in which discovery, triage, and response may all begin moving at a very different pace.
Post Syndicated from Светла Енчева original https://www.toest.bg/anahronizum-zhenite-v-predizbornite-programi-prez-2026-g/

Жените в България са близо 51,9% по данни на НСИ. Как партиите и коалициите, които се състезават за 52-рото Народно събрание, си представят мястото им в обществото? Какви са позициите им по теми като равенство между половете, феминизъм, домашно насилие, майчинство, аборти? Какво е отношението им към мерките спрямо жените в европейското законодателство? Например какво планират във връзка с Директивата за прозрачност на заплащането в ЕС, която ще се транспонира в държавите членки на 1 юни 2026 г., тоест ще трябва да започне да се прилага след по-малко от два месеца? Или такива неща са им под радара?
През 2021 г. анализирах отношението към жените в предизборните платформи на партиите и коалициите, които според проучванията имаха шанс да влязат в парламента. През 2026 г. реших да прегледам програмите на всички партии и коалиции, участващи в изборите. Причините за това са три:
Първо, по време на предварителното проучване установих, че политическите субекти, за които се очаква да преминат 4-процентовата бариера, не са казали много за жените. Второ, когато прогнозите са в рамките на статистическата грешка, са възможни изненади. Трето, в изборите участват и партии и коалиции, за които ние, избирателите, не знаем почти нищо. Защо да не проучим позициите им по някоя тема?
 Светла Енчева

Някои коалиции имат обща програма, други – не. Някои партии са с остарели програми и платформи, други нямат никакви, трети разполагат с програмни документи, които са сякаш извън времето. Или с писания със странни заглавия, за които не е ясно програма ли са, или не. Реших да се ръководя от следните принципи:
Темите, свързани с жените, се опитвам да идентифицирам по следните ключови думи (както и техните производни): жена, пол, равенство, равнопоставеност, феминизъм, стъклен таван, насилие, майка, родилка, раждане, родители, аборт. След известно колебание реших да включа и раждаемостта. Въпреки че се асоциира предимно с темата за демографията, тя е свързана с изискване към жените, а именно – да раждат повече деца.
Надежда Цекулова
В дългата 143 страници програма на политическия проект на Румен Радев, спряган за победител на предстоящите избори, жените се споменават в прав текст само веднъж:
Целенасочени инициативи за насърчаване на предприемачеството сред млади хора и жени в технологичните и иновативните сектори.
Еднократно се споменават и „гарантиране на равенство между двата пола“ (важно е да се уточни колко са половете, да не би някой да си помисли, че са повече от два), „майчино […] здравеопазване“ и „насърчаване на раждаемостта“. Пет пъти става дума за родители и родителство, без да се уточнява пол. И това е.
На страницата на партията на Бойко Борисов са налични презентация на предизборната програма от 2026 г. с обем от 65 слайда, както и пълна версия на програмата от 2024 г. (31 страници). Единственото, което се казва в презентацията, без да се визират конкретно жените, е, че инвестициите в детски ясли, услуги за грижа за деца и гъвкави форми на заетост „ще позволят по-добро съчетаване на родителството и професионалния живот“. В програмата от 2024 г. два пъти се споменава, че домашното насилие ще е приоритет. Също два пъти става дума за родители, отново без да се уточнява полът им.
За разлика от 2024 г., за предстоящите избори партиите от ПП–ДБ нямат обща платформа. Две от трите партии в коалицията имат собствени актуални програмни документи.
Предизборната програма на „Продължаваме промяната“ се свежда до т.нар. Протокол за ликвидация на корупцията. Това е листовка от две непълни страници, в която темата за жените очаквано не е намерила място.
„Да, България“ предлага цели два документа – платформа от 53 страници, озаглавена „Силна България в силна Европа“, и „Програма за противодействие и превенция на корупцията и за върховенство на закона“. В общата платформа два пъти се споменава майчиното здраве. Шест пъти се говори за родители (включително възрастни и приемни). За насилие, но само по отношение на децата, става дума два пъти. Не е изненада, че в антикорупционната програма не се казва нищо, свързано с жени.
На сайта на ДСБ няма актуална програма, а кратка извънвремева платформа. В нея не става дума за нищо, свързано с жени. Веднъж се споменават родители в контекста на социално слаби хора, а за равенство става дума седем пъти, но нито веднъж това не е свързано с пола.
Светла Енчева
В предизборната програма на ръководеното от Делян Пеевски ДПС жените не се споменават, но за майки става дума шест пъти и им се дават големи обещания: „чухме майките“ (чути са и бащите, както и още десетина групи хора), „нулев данък за майки с две и повече деца“, „майчински фондове […] в помощ на младите майки“, „майчиното […] здравеопазване“, „[в]ременен осигурителен стимул за работодатели, които наемат/връщат родител след майчинство/бащинство (6–12 месеца)“. Говори се за подкрепа на раждаемостта, инвестиционна сметка при раждане на първо дете (може би идея, заимствана от Тръмп) и еднократна помощ в размер на една средна работна заплата за всяко следващо. Шест пъти се споменават и родителите, без да се уточнява полът. Два пъти става дума за домашно насилие, като в единия случай то е конкретно към деца, а в другия се представя като форма на „битова престъпност“.
В дългата 97 страници програма на партията на Костадин Костадинов жените не се споменават. Като изключим определението на българската земя като „майка-кърмилница“, за майки става дума само веднъж – в качеството им на възрастни жени с ниски пенсии. За пол се говори два пъти – в контекста на неодобрението на смяната на пола и на задължителната военна служба. Насилието е само в задължителните ваксинации и по отношение на децата и младежите. За раждаемост и раждане става въпрос седем пъти, като навсякъде контекстът е, че раждаемостта е ниска и трябва да се повиши. За родители – девет пъти, без да се визират конкретно майките. Според „Възраждане“ например в училище трябва да се учи как да бъдем „добри родители“, трябва да има данъчни стимули „за многодетни семейства при работещи родители“, но пък санкции
за недобросъвестни родители, които не възпитават децата си правилно и […] ги тласкат в лапите на порока.
Платформата за предстоящите избори на оглавяваната от Крум Зарков партия е от 10 страници. В нея не става дума нито за жени, нито за майки, нито за насилие, нито дори за родители. Споменава се обаче, че се раждат все по-малко деца и трябва да се насърчава раждаемостта. Когато пък дойде победата над „неолибералния модел, подвластен на олигархичния капитализъм“, ще настъпи бъдеще, „в което равноправието, сигурността и закрилата на правата и законните интереси на всеки човек ще бъдат поставени на първо място“. Един вид, като дойде комунизмът, всички ще са равни – защо да говорим специално за жените?
Светла Енчева
На сайта на ИТН пише, че програмата е за 2026 г., но тя е по-скоро за 2023 г. В подкрепа на тази хипотеза е не само името на страницата programa-2023, което може да се види в адресното поле на браузъра, а и съдържанието ѝ: призовава се например за електронно дистанционно гласуване – без никакъв намек, че групата на ИТН в 51-вото Народно събрание се обяви против машинния вот. Откогато и да датира програмата обаче, в нея не става дума за жени и майки. Веднъж се споменава раждаемостта – във връзка с „демографската криза“. Казва се, че родителите трябва да са „фактор във възпитателния процес“, говори се за „недостатъчни родителски умения“ и „програми, подготвящи младите хора за бъдещото родителстване“.
Партията на Ахмед Доган предлага както предизборна платформа, така и програма. И двете не са датирани. В тях не става дума за нищо, свързано с жени и майки. Веднъж се споменава „подкрепа за работещи родители“.
На сайта на партията на Радостин Василев има страница с приоритети, без да става ясно какво стои зад всеки от тях, така че не се знае има ли МЕЧ някакво отношение към жените.
Предизборната програма на партията на Ивелин Михайлов се нарича „20-годишен план за възстановяване на България“ и е под формата на презентация от 48 слайда. Нищо свързано с жени, майки или пък с която и да е от ключовите думи, по които преглеждам програмите, не намира място в този 20-годишен план. Все пак има жени на картинки, обаче изобразените мъже са повече.
Партиите и коалициите, които не са парламентарно представени (с изключение на „Прогресивна България“), съм разделила в няколко групи според типа им (коалиция или партия), както и според наличието или липсата на предизборна програма. Вътре в групите политическите сили са подредени в съответствие с номера им в бюлетината.
В програмата на „Синя България“ не става дума за майки, но два пъти се споменават жените, все в анти-ЛГБТИ контекст (оригиналният правопис е запазен):
Във втория от тези цитати става дума и за пол, освен това се говори и против „ЛГБТ и нахлуването на половата идентичност в обществото“.
Равнопоставеността се споменава веднъж – като противовес на малцинствените групи: „Държавата не може да фаворизира отделни групи, малцинства или сдружения със специални права и социални привилегии, за сметка на равнопоставеността на всички.“
Светла Енчева
В подобен дух се тематизира и насилието: „Ние осъзнаваме нуждата в една европейска, християнска демокрация да защитим различията от насилие и дискриминация, но сме категорични, че защита на индивида не означава диктатура на малцинствата.“ Споменават се „родителска апатия“ и „родители на ученици“.
Накратко, програмата на „Синя България“ не обещава нищо на жените, но има претенция какви да бъдат те – да не са трансджендър, да са хетеросексуални и да не претендират за „специални права“.
Програмата на „Антикорупционен блок“ не съдържа нищо, свързано с жените.
Коалиция „Моя България“ няма общ сайт. Тя се състои от Зелената партия, „Нова сила“ (която няма сайт) и Български национален демократичен съюз „Целокупна България“.
Няма сайт и коалиция „Трети март“, както и една от партиите в нея – „Благоденствие – обединение – градивност“. Друга от тях – „За велика България“ – има сайт, но в него няма програма, а само кратко описание на профила на партията. Третата – Партията на българските жени – има сайт, информацията в който е актуална за далечната 2005 година. От нея може да се разбере, че партията е „първата по рода си женска формация“ и идеите ѝ „не са феминистки“, а християнски, в духа на традиционните ценности, „чийто най-голям радетел е била и е българската майка“. Не става ясно обаче какво предлага на жените Партията на българските жени.
Коалиция „Сияние“, която според проучванията е все по-близо до 4-процентовата бариера, също няма сайт, както и една от двете партии, осигуряващи регистрация за изборите – „Общество за нова България“. Изброените политики на другата партия – „Волт“, са актуални за местните избори през 2019 г. В тях жените не са тема.
Светла Енчева
„Пряка демокрация“ има на сайта си платформа, която всъщност е книга с обем от 256 страници, актуална за 2024 г. и издадена от председателя на партията Петър Клисаров. В нея за жени става дума четири пъти, от които нито веднъж с добро:
От друга страна, авторът иска да бъдат „изгонени“ от социалната политика „многодетните майки, превърнали майчинството в бизнес“ (този израз се споменава два пъти в програмата). Но иначе според него има нужда от „закрила на майчинството“, и казва, че майчината „и перинаталната смърт [мъртвородените деца – б.а.] у нас все още е над 2 пъти по-висока от средното равнище в ЕС“.
В програмата се казва също, че момичетата имат нужда от игри, „свързани главно с имитацията на майчинството“, което обаче не означава, че двата пола трябва да играят отделно през цялото време, и че „нашите възгледи категорично отричат джендърното обучение“. Предлага се увеличение на срока на паричното обезщетение при бременност и раждане и изграждането на перинатални центрове, увеличаване на плащанията и отпуска за майчинство, но само за второ дете. Също и програма „Майчин капитал“ – „по примера на руската“, в която на майките или на самотните бащи да се предоставят средства за точно определени цели, и повече ясли и детски градини „за отмяна на работещите майки“. Предвижда се и „специална програма за повишаване на раждаемостта“.
Светла Енчева
В платформата на „Пряка демокрация“ се говори и за „регрес“ в образованието, довел до „опростачване, феминизиране и деградация на учителското съсловие“, и за „неправилния полов живот в ранна възраст“.
Партия „Нация“ има недатирана програма, в която няма нищо, свързано с жените, но се говори за „защита на традиционното семейство“ и „противопоставяне на либералните ЛГТБ „ценности“, които развращават младите и унищожават основата на НАЦИЯТА и националната държава“ (оригиналният правопис е запазен).
На сайта на „България може“ са изброени десет приоритета, един от които е „доживотна отмяна на данък общ доход за майките с 3 или повече деца!“.
Партията на зелените разполага с два недатирани документа – изборна платформа и идейна програма. Новата цел на обществото според партийната платформа включва равни права на всеки гражданин в България, независимо от пола. В програмата се говори за „равнопоставено участие на жените“. Родителите се споменават веднъж – във връзка с материалното им състояние. За насилие става дума пет пъти, но без връзка с пола, а за раждаемост – три пъти, в контекста на необходимостта от увеличаването ѝ.
Програмата на „Глас народен“ не е датирана, но е написана най-късно през 2012 г., когато СДС и ДСБ, споменати като общ политически субект, престанаха да бъдат в коалиция.
Народна партия „Истината и само истината“ има сайт, но няма програма. Движението на непартийните кандидати, партията на Корнелия Нинова Национално движение „Непокорна България“ и партия „Съпротива“ нямат сайтове.
Жените все по-малко са тема за българските политически субекти в сравнение с 2021 г. За пет години те са изчезнали от предизборните програми на „Демократична България“ (днес в коалиция с „Продължаваме промяната“), БСП и ИТН. Равенството на половете почти не е тема, домашното насилие се споменава единствено в програмата на ГЕРБ от 2024 г. (и от ДПС, но само във връзка с децата). Доколкото става дума за жени в платформите, то е най-вече във връзка с родителството и раждаемостта.
В същото време се наблюдава засилване на ултраконсервативните наративи – жените са сведени предимно до произвеждането на деца с цел подобряване на демографската ситуация. Единствената програма, в която става по-подробно дума за тях – тази на „Пряка демокрация,“ – обрисува картина, подобна на „Разказът на прислужницата“. Търсейки по зададените ключови думи, нееднократно се натъквах на расистки, хомофобски и трансфобски послания. Против хомофобията се обявява само „Глас народен“, чиято програма е отпреди 14 или повече години.
Светла Енчева
От друга страна, от заявяването на нещо в програмата на дадена политическа сила не трябва да се правят изводи, че тя има намерение да го осъществи, а още по-малко – че го прави или ще го направи. Пеевски едва ли ще реализира всички чудеса, които обещава на майките (и на останалите групи от населението). В платформата на „Прогресивна България“ се говори за „равенство между двата пола“, но при 31 избирателни района само шест от водачите на листи са жени, а на предизборните събития жените около Румен Радев са малцинство.
Корнелия Нинова от своя страна се похвали, че 51% от водачите на листите на партията ѝ „Непокорна България“ са жени, но пък няма програма, от която да стане ясно какво предлага формацията за жените. Известни са обаче пораженията, които Нинова нанесе на борбата срещу насилието над жени. „Глас народен“ се обявява против хомофобията, но Светльо Витков има подигравателни песни за гей хората.
Ала макар и с тези уговорки – докато всички се борят с корупцията, темата за правата на жените все повече липсва в българския политически живот. А това отваря вратата към ограничаването им.
Post Syndicated from LGR original https://www.youtube.com/watch?v=MzlX53Bdj6s
Post Syndicated from Jeronimo De Leon original https://www.backblaze.com/blog/data-orchestration-in-the-age-of-autonomous-agents-architectural-patterns-building-on-nemoclaw-openclaw/
OpenClaw crossed 250,000 GitHub stars in 60 days, surpassing React’s decade-long record to become the most-starred software project on GitHub. At GTC 2026, NVIDIA CEO Jensen Huang declared it “the operating system for personal AI” and told the room: “For the CEOs, the question is, what’s your OpenClaw strategy?”
At NVIDIA’s Hack for Impact hackathon at GTC, I built and watched engineers build autonomous agents on NemoClaw, OpenClaw, and Nemotron. Wildfire detection ingesting NASA satellite data. Crime pattern analysis across police jurisdictions. Energy grid anomaly forecasting.
The same architectural question surfaced in every project: agents that collect and generate data at scale need a deliberate strategy for archiving, retaining, and surfacing that data. Without one, agent-produced artifacts become dark data, generated but inaccessible, unversioned, and invisible to the rest of the organization. That question only gets more consequential in production.
NVIDIA’s NemoClaw wraps OpenClaw with security through OpenShell, a runtime that sandboxes each agent at the kernel level. Network requests, file access, and inference calls are governed by declarative YAML policy, enforced outside the agent’s process so the agent itself can never override them.
OpenClaw agents create workspace files (SOUL.md, USER.md, IDENTITY.md) that define the agent’s personality, preferences, and behavioral context. Inside a NemoClaw sandbox, this state lives in a Kubernetes Persistent Volume Claim inside an embedded K3s cluster, and the community is already asking for better backup and restore workflows on the NemoClaw GitHub repo.
At fleet scale, with dozens of agents each maintaining persistent memory, conversation history, and skill artifacts, a durable storage layer beneath the runtime is what keeps agent state from becoming disposable. What that layer looks like depends on the type of data your agents produce.
Two categories of data define the storage requirements for autonomous agents.
Autonomous agents generate reports, analyses, transformed datasets, alerts, and increasingly, multimodal outputs like processed video, audio, and images. Inside NemoClaw’s sandbox, filesystem access is confined to /sandbox and /tmp, both ephemeral by design.
Cloud storage decouples the artifact from the runtime, enables scoped access via URLs, and plugs into every major orchestration framework. Bucket-level permissions and scoped application keys extend governance into the storage layer, so each agent or agent class gets write access only to its designated output path.
Lineage matters here too: Each artifact should trace back to which agent, model, inputs, and policy produced it. Our GTC project, FireWatch, used Backblaze B2 exactly this way, uploading wildfire risk reports with a bucket-scoped key, generating shareable URLs, and embedding them directly in stakeholder alert emails.
Agent memory, skill artifacts, and audit logs from policy decisions all require durable, long-term retention. NemoClaw’s privacy router splits inference between local and cloud models based on policy, generating routing metadata that compliance teams will want to retain and query. Cloud storage brings high durability, append-only immutability for audit trails, and lifecycle policies for tiered retention as data ages.
We built an open source OpenClaw plugin (openclaw-b2-backup) around this: Encrypted snapshots of agent config, memory, and sessions pushed to B2 on a daily cron, before compaction events, and on gateway shutdown. Three fields to configure, rollback from chat, one-command migration to a new machine.
The open-source, autonomous AI agent ecosystem now spans at least 16 variants, each optimized for a different deployment context: NanoClaw for container-isolated security, ZeroClaw for edge deployment in a 3.4MB Rust binary, IronClaw for regulated industries through Trusted Execution Environments, managed platforms like ClawCloud and Maxclaw, and Qwen-Agent from Alibaba for the Chinese developer ecosystem.
Whether self-hosted or managed, all of them produce artifacts that need to persist beyond the runtime. Teams building autonomous agents for their organizations will need durable output sharing, state backup, and cross-agent data access regardless of which runtime they choose.
Architect your agent data orchestration on cloud storage. As organizations scale from initial agent deployments to multi-team production workloads, data volume grows with every agent added, every week they run, and every modality they process. Agents gather, generate, and transform data continuously. Cloud storage gives you a durable layer for managing that lifecycle: ingestion and collection, versioned outputs, long-term archival, lifecycle policies for retention, and portability across agent platforms as your organization’s runtime choices evolve. Establishing this now, while the ecosystem is still forming, is the strategic move.
Automate agent state backup as part of your deployment standard. Agents building context across customer data, internal systems, and team workflows for weeks carry real operational value. Automated workspace snapshots protect that investment, create a disaster recovery path, and enable migration across environments.
Design for lineage and audit from day one. Policy decisions, tool invocations, inference routing, and multimodal processing chains all generate metadata. For enterprises operating under SOC 2, HIPAA, or GDPR, storing lineage and audit data alongside your artifacts in cloud storage means your compliance posture is ready before the audit, not after.
NemoClaw brought governance to the agentic stack. If your organization is deploying autonomous agents today, data orchestration and lineage are your next architectural decisions. Get them right early, and your agents scale with durable state, shareable outputs, and auditable history from day one.
The post Data Orchestration in the Age of Autonomous Agents: Architectural Patterns Building on NemoClaw & OpenClaw appeared first on Backblaze Blog | Cloud Storage & Cloud Backup
Post Syndicated from Crosstalk Solutions original https://www.youtube.com/watch?v=nq_rZNucgPI
Post Syndicated from Stephan Schiller original https://aws.amazon.com/blogs/big-data/introducing-amazon-msk-express-broker-power-for-kiro/
Developers working with Amazon Managed Streaming for Apache Kafka (Amazon MSK) regularly need to make decisions that require deep operational context—choosing the right instance type, diagnosing consumer lag, or planning for a traffic spike. Answering these questions means piecing together documentation, metrics, and operational know-how.
What if your IDE could guide you through that workflow with built-in domain expertise and tooling? Kiro is an AI-powered agentic IDE that lets you describe what you need in natural language. Whether it’s infrastructure configuration or operational troubleshooting, Kiro guides you through the solution.
In this post, we’ll show you how to use Kiro powers, a new capability that equips Kiro with contextual knowledge and tooling. You can simplify your MSK cluster management, from initial setup to diagnosing common issues, all through natural language conversations.
Amazon MSK Express Brokers are a fully managed offering where AWS handles much of the underlying infrastructure. However, platform teams still need to correctly size clusters based on throughput requirements. They also need to understand the right Amazon CloudWatch metrics during performance issues and investigate when CPU usage or replication lag is higher than expected. MSK best practices documentation spans multiple AWS guides. This makes it time-consuming to find relevant information during production incidents. New team members face a learning curve with MSK operations and can repeat common sizing and configuration mistakes.
Although Express Brokers simplify infrastructure management, you still face operational challenges that require deep Kafka expertise across three areas:
These challenges mean that setting up an MSK cluster, analyzing slow-running clients, or investigating high-CPU load requires pulling together documentation, configuration details, CLI tooling, and operational know-how, which is often spread across multiple sources. Kiro powers address these challenges by bringing best practices, guided workflows, and tooling directly into your IDE, reducing the expertise barrier and the time spent context-switching between documentation, consoles, and the CLI.
Kiro powers is a feature that combines best practices, specialized context, and tool integrations into a single capability. You can install powers with one click in the Kiro IDE or add them from a public GitHub URL. Each Power combines the following components:
The key advantage of Kiro powers is that they load context dynamically based on the user’s task. Instead of configuring every MCP server upfront and re-providing context in each conversation, powers activate the right tools and knowledge on demand. This keeps your agent’s context focused and relevant. In the next section, we look at how these components work together specifically for MSK Express Broker operations.
The MSK Express broker power packages the AWS MSK MCP server with targeted streaming operations guidance, giving your Kiro agent expertise for MSK Express Broker operations and cluster management. You can use it to build Kafka-based streaming applications through Kiro while maintaining Express broker best practices throughout the development lifecycle.
For cluster operations, you can create Express broker clusters, monitor health metrics, and manage configurations through natural language. You can retrieve cluster metadata, check broker endpoints, and verify replication status. The Power also supports operational monitoring. You can track CPU utilization, throughput limits, partition distribution, and AWS Identity and Access Management (IAM) connection metrics.
To see how this works in practice, here’s what happens when you interact with the Power: When you ask Kiro to create an MSK cluster, the Power recommends appropriate instance sizes based on your throughput requirements. When you’re troubleshooting, it knows to check LeaderCount before diving into network metrics. When you’re troubleshooting authentication failures, it recommends client settings like reconnect.backoff.ms and group.instance.id to resolve connection churn and rebalancing issues against Express broker limits. Use cases include:
The MSK Express broker power brings together documentation, metrics, and operational context so your Kiro agent can correlate findings and help identify root causes specific to your infrastructure.
Starting with Kiro powers takes only a few clicks in the Kiro IDE. You can install from the built-in marketplace or import from a public GitHub URL. Kiro packages all components and makes them available to the Kiro agent.
To set up the MSK Express broker power, follow these steps:
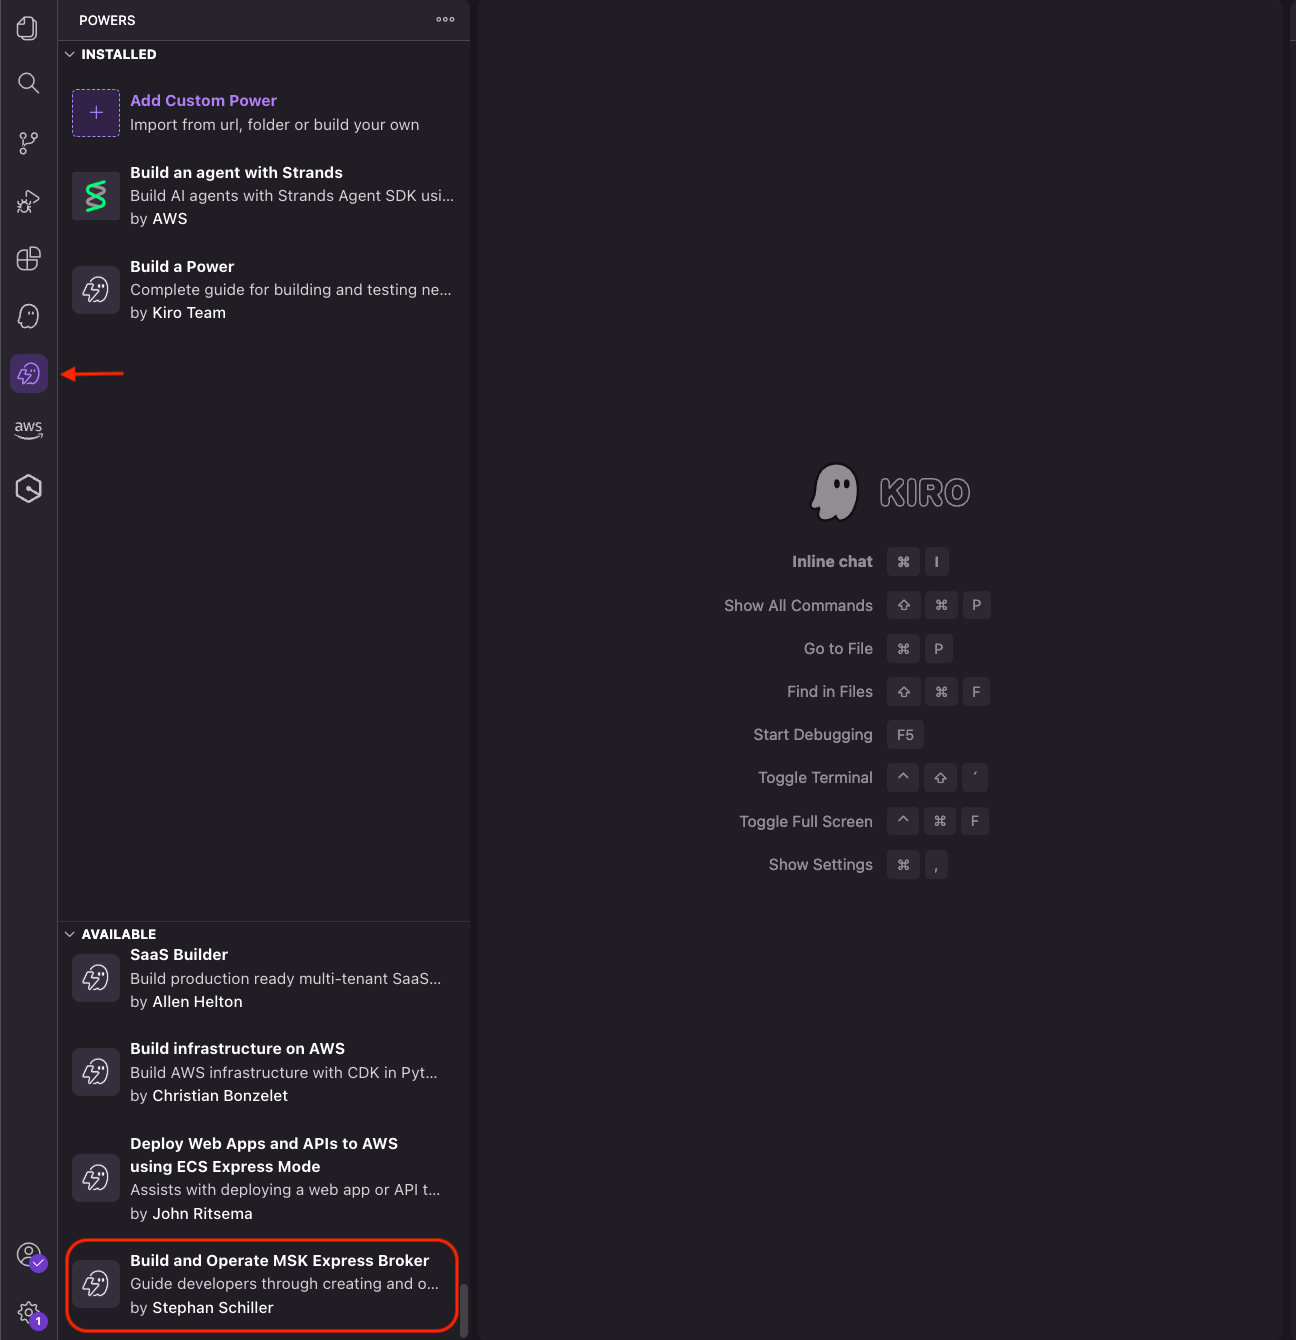
You can also visit the Kiro powers marketplace to explore other powers.
The MSK Express broker power streamlines Kafka operations by combining Model Context Protocol (MCP) servers with operational guidance. With natural language interactions, you can create clusters, monitor health, optimize configurations, and troubleshoot issues without reviewing extensive documentation.
Install the MSK Express broker power in your Kiro IDE and learn more about Kiro and available Kiro powers.
Post Syndicated from Искрен Иванов original https://www.toest.bg/ami-ako-usa-izlyazat-ot-nato/
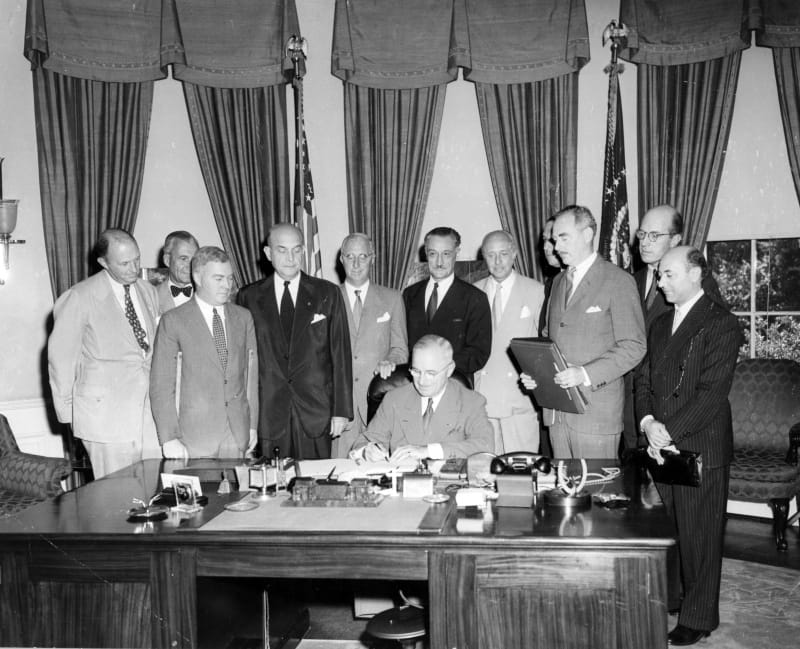
Когато американският президент Хари Труман подписва Договора от Вашингтон, с който се създава Организацията на Североатлантическия договор едва ли някой в САЩ е предполагал, че десетилетия по-късно Америка може да поиска да се изтегли едностранно от НАТО.
Този исторически паралел много напомня на броженията срещу американските бази у нас. Всички помним прословутите протести от 1999 г. със скандиранията „НАТО вън!“, в които участваха политици, по-късно сами определили членството на България в Алианса като стратегическа цел. Та така и досега.
Разпадането на НАТО винаги е било мечта за тези, които искат да видят края на една колективна система за сигурност, благодарение на която вече близо 80 години Европа се радва на относително спокойствие. Относително не защото НАТО е в толкова слаба позиция, колкото ни убеждават, а защото и днес, подобно на първите години след 11 септември 2001 г., има амбициозни политически лидери от двете страни на Атлантика, готови да поставят вътрешнопартийния си интерес над националния.
Искрен Иванов
Дори критиците на Алианса не могат да отрекат една съществена разлика между него и класическите военни съюзи. Варшавският договор и дори съюзните споразумения, които САЩ имат с азиатските си партньори, почиват върху междуправителствения принцип на координация и взаимни консултации. Алиансът е нещо повече.
НАТО е уникален заради колективната система за сигурност – членството в него предполага взаимни ангажименти, по силата на които атаката срещу един съюзник ще се възприема като атака срещу всички съюзници.
Този отличителен белег на Алианса обаче носи със себе си и голяма отговорност – член 3 от Вашингтонския договор, съгласно който съюзниците са длъжни да развиват отбранителните си способности, за да може НАТО да функционира.
Член 3
За по-ефективно постигане на целите на настоящия Договор страните по него, поотделно и съвместно, като развиват непрекъснато и ефективно собствените си възможности и си оказват взаимна помощ, ще поддържат и развиват своите индивидуални и колективни способности да се противопоставят на въоръжено нападение.
Член 3 и член 5 следователно са гарант, че тази колективна система за сигурност се поддържа от всички и функционира за всички – принцип, който изисква солидарно споделяне на финансовата тежест и отбранителните ангажименти в Алианса.
Вторият фактор за успеха на НАТО е ядреното възпиране, и по-конкретно тактическите ядрени оръжия, които САЩ са разположили на европейския континент, за да удържат възможна агресия от друга ядрена сила. Без този ядрен чадър отбранителният капацитет на НАТО остава конвенционален, но недостатъчен, за да възпре заплахите от държави като Русия и Северна Корея.
Франция и Великобритания разполагат с ядрен арсенал, но не биха могли да гарантират отбраната на континента в степента, в която могат САЩ, не само защото нямат ядрен паритет с Русия, но и защото Лондон и Париж ликвидираха ядрените си триади след края на Студената война.
Александър Малинов
Това поставя НАТО в силна зависимост от Вашингтон и от политиката на президентските администрации, които управляват САЩ. И тъй като обикновеният американски избирател не се интересува какво се случва извън държавата му, освен ако тя не бъде нападната, общественото мнение в САЩ няма отношение доколко конкретната американска администрация подкрепя европейските си съюзници.
Самата идея, че французи и германци могат да извършват съвместни военни учения под един флаг, би изглеждала немислима само преди столетие. Същото се отнася за Париж и Лондон, станали неволни съюзници срещу Берлин в двете световни войни. Какво остава за Централна и Източна Европа, които в продължение на цялата Студена война участват в друга колективна система за сигурност, чиято стратегическа култура значително се отличава от западната.
Въпреки че в първите години на Алианса са съществували множество спорни въпроси относно това защо Америка трябва да бъде основният източник на средства за отбранителния бюджет на НАТО, дебатът придобива съществени измерения след разпадането на СССР, когато образът на врага изчезва и е заменен с глобалния тероризъм.
Искрен Иванов
Първият очевиден отговор е мир. Тази дума звучи изключително утопично за по-младото поколение, макар че то не помни ужасите на Втората световна война, а за периода преди нея знаем само от учебниците по история. Снимките на сринатия до основи Берлин, окупирания от нацистите Париж, концентрационните лагери на смъртта и разбира се, съветската окупация на Централна и Източна Европа изглеждат реалистично, но съвсем друго е усещането, когато тези събития са преживени от първо лице. Голяма част от хората, които са били част от тях обаче, вече не са между живите.
Второто очевидно предимство на НАТО, което е и най-критикувано от неговите противници, е стабилността. Когато една организация предоставя на даден съюзник механизми за консултация в случай на заплаха за сигурността, това създава ясни предпоставки за координиран отговор срещу потенциална атака. Такъв е характерът на консултациите, които присъстват в Договора за отбрана, или т.нар. Договор за силен съюз между САЩ и Република Корея, както и механизмите, предвидени в Договора за взаимно сътрудничество и сигурност между Вашингтон и Токио.
Но когато тези механизми регламентират гаранции за взаимната защита на отделните съюзници, тогава стабилността на един пакт е пряко следствие само по себе си от неговото съществуване. С други думи, НАТО и гаранциите, които то дава, предоставят на Европа свободата да се занимава с всичко друго, но не и със собствената си сигурност.
А що се отнася до САЩ, за тях НАТО е не просто непосилно бреме, а инструмент за влияние върху баланса на силите в глобалната политика. Самото понятие за американско глобално лидерство почива върху съюзите, които Вашингтон изгражда след края на Втората световна война, а разширяването на Алианса довършва тази символична победа на Запада в Студената война. Ангажиментите на Америка към НАТО ѝ гарантират, че тя няма да остане откъсната от ставащото на Стария континент, да не говорим че проблемите на Европа – в сегашния все по-глобализиращ се свят – могат сериозно да повлияят на американската национална сигурност, в случай че Североизточното крайбрежие на САЩ остане оголено.
Александър Нуцов
За Европа отговорът на този въпрос е очевиден. В случай че Америка реши да се изтегли от Алианса, Европейският съюз ще трябва бързо да мобилизира свои сили за бързо реагиране, с които да се противопостави на потенциална провокация от страна на Русия. Важно е да подчертаем, че Москва едва ли би се наела директно да хвърли ръкавицата на Европа, тъй като все още воюва в Украйна, а и армиите на европейските държави не са толкова нискотехнологични, за колкото ги смята Доналд Тръмп.
За да бъдат напълно сигурни европейците, че подобни провокации няма да бъдат успешни, проектът за френски ядрен чадър трябва да включва не само гаранции от страна на Париж, но и възстановяването на френската ядрена триада. Това е дълъг и сложен процес, който не може да завърши в рамките на година, освен ако в него не бъде интегрирана Германия или ако френският ядрен потенциал не бъде споделен с това, което е останало от НАТО.
Нещо повече, едно евентуално изтегляне на САЩ от НАТО ще налее вода в мелницата на някои особено крайни популисти, така че управляващите европейски елити трябва да имат дяволски добра икономическа формула срещу техните аргументи.
САЩ няма да усетят загубите от изтеглянето си веднага, а едва след като то напълно стане факт. След като Америка изтегли войските и ядрения си потенциал от Европа, нейният военнопромишлен, икономически и индустриален комплекс по Североизточното крайбрежие ще остане уязвим. В тези условия САЩ ще трябва или да се насочат към двустранни съюзи с бившите си натовски съюзници, или да гарантират интересите си в Европа с помощта на принуда – установявайки контрол върху стратегически важни региони като Гренландия, от които да проектират сила към Русия, Китай и Стария континент едновременно.
Готовността на Доналд Тръмп да воюва срещу целия свят не трябва да се подценява, но готовността на Америка, от друга страна, трябва. Сред най-разрушителните последици от такова решение ще бъде и фактът, че Америка ще загуби цялото си геополитическо влияние в ключови региони, което ще даде възможност на Китай сравнително бързо да излезе начело.
Велизар Шаламанов
Най-големият губещ от разпадането на НАТО обаче ще са страните от Източна Европа, които ще се окажат в позицията на Украйна по време на Евромайдана. По същество последиците няма да бъдат непосредствено свързани с някаква загуба на суверенитет, а по-скоро с
Твърде е възможно в Европа да се появят и държави, които да продължат военното си сътрудничество със САЩ, но това сигурно ще бъдат единици, като Полша например – тя е от страните със силна и добре развита икономика, сравнима със западноевропейските.
В тези условия България отново ще се окаже на входа на нов преход, този път между членството си в ЕС, Борда за мир на Тръмп и възможното възстановяване на отношенията с Русия.
Член 13 от Вашингтонския договор регламентира правото на всеки съюзник да се изтегли от НАТО, като предварително уведоми за това американското правителство и получи едногодишен логистичен срок, за да осъществи процедурата.
Член 13
След изтичане на двадесет години от влизането на Договора в сила всяка от страните по Договора може да престане да бъде страна по него след изтичане на една година от датата, на която нейното известие за денонсиране на Договора е било предадено на правителството на Съединените американски щати, което ще уведомява правителствата на останалите страни по Договора за всяко депозиране на такова известие за денонсиране.
Очевидно е обаче, че ако САЩ сами напуснат НАТО, това би означавало, че Алиансът в стария си вид нa практика се саморазпуска. Твърде е вероятно Вашингтон да бъде последван от Канада, която на няколко пъти показа, че въпреки различията си с Тръмп не желае да жертва спокойствието по границите си, за да изпитва търпението му.
Искрен Иванов
Същевременно съществуват някои законови бариери пред тези действия, като най-сериозната от тях е т.нар. National Authorization Defense Act от 2023 г., подписан от бившия президент Джо Байдън. Той забранява на държавния глава едностранно да изтегли Америка от НАТО, без да е получил одобрението на 2/3 от Сената или без Конгресът да е приел специален закон за оттеглянето на САЩ от Алианса. На този етап такова мнозинство няма нито сред демократите, нито сред републиканците, което прави подобно гласуване обречено на провал, а приемането на евентуален закон за изтегляне от НАТО – невъзможно.
И все пак президентът може да се позове на чл. 2 от Конституцията на САЩ, който регламентира изричното му право да сключва договори с чужди правителства. От 1978 г. повечето президенти започват да тълкуват този член и по обратния начин – че това право се разпростира и върху оттеглянето от подобни споразумения. Върхът в това отношение е решението на президента Джими Картър да оттегли дипломатическото признаване на САЩ за Тайван в полза на Пекин, като по този начин слага край на Договора за взаимна отбрана между Вашингтон и Тайпе.
Така се отваря възможността следващите президенти да използват прецедента свободно. В същото време група сенатори начело с Бари Голдуотър завежда във Върховния съд дело против държавния глава с мотива, че действията му вредят на САЩ. След това Върховният съд не се произнася по случая, което допълнително дава свобода на американските президенти да маневрират в политиката си относно споразуменията в сравнително широки граници.
Казано накратко, дори Доналд Тръмп да се позове на Конституцията и на правото си да упражнява член 2 от нея, тя не му дава основания едностранно да прекрати членството на Вашингтон в НАТО без подкрепа от Сената или от Конгреса като цяло. Такова действие почти веднага би породило реакция от страна на Върховния съд, чието решение ще бъде съдбоносно за евроатлантическото единство.
Искрен Иванов
Съвсем отделен е въпросът, че ако сегашната президентска администрация не желае да поеме ангажимент към член 5 на Вашингтонския договор, Европа трудно може да разчита на Тръмп поне до края на мандата му. Нещо повече, авторитетът на Алианса вече е сериозно накърнен, което крие опасност за неговата ефективност, освен ако Европа не покаже пред света, че може да се защитава сама.
За жалост, твърде възможен е и следният сценарий: Европа за пореден път да изпълни исканията на американския президент, макар и по по-завоалиран начин. Почвата за това вече се подготвя от британската дипломация. Преди дни в Лондон беше свикана междуправителствена среща за обсъждането на кризата с блокирането на Ормузкия проток. В крайна сметка изглежда, че нито САЩ, нито Европа и Великобритания имат полза от западането на НАТО. И дори Тръмп го знае.
Post Syndicated from daroc original https://lwn.net/Articles/1066581/
The idea of using large language models (LLMs) to discover security problems is
not new. Google’s Project Zero
investigated
the feasibility of using LLMs for security research in 2024. At the time, they
found that models could identify real problems, but required a good deal of
structure and hand-holding to do so on small benchmark problems. In February
2026, Anthropic
published a report
claiming that the company’s most recent LLM at that point in time, Claude Opus 4.6, had discovered
real-world vulnerabilities in critical open-source software, including the Linux
kernel, with far less scaffolding. On April 7, Anthropic announced a new experimental model that is
supposedly even better; which they have
partnered with the Linux Foundation
to supply to some open-source developers with access to the tool for security reviews.
LLMs seem to have progressed significantly in the last few months, a change
which is being noticed in the open-source community.
Post Syndicated from jzb original https://lwn.net/Articles/1066926/
The Free Software Foundation has published
a short article on relicensing versus license compatibility.
The FSF’s Licensing and
Compliance Lab receives many questions and license violation reports
related to projects that had their license changed by a downstream
distributor, or that are combined from two or more programs under
different licenses. We collaborated with Yoni Rabkin, an experienced
and long time FSF licensing volunteer, on an updated version of his
article to provide the free software community with a general
explanation on how the GNU General Public License (GNU GPL) is
intended to work in such situations.
Post Syndicated from jzb original https://lwn.net/Articles/1066972/
Security updates have been issued by Debian (firefox-esr, postgresql-13, and tiff), Fedora (bind, bind-dyndb-ldap, cef, opensc, python-biopython, python-pydicom, and roundcubemail), Slackware (mozilla), SUSE (ckermit, cockpit-repos, dnsdist, expat, freerdp, git-cliff, gnutls, heroic-games-launcher, libeverest, openssl-1_1, openssl-3, polkit, python-poetry, python-requests, python311-social-auth-app-django, and SDL2_image-devel), and Ubuntu (dogtag-pki, gdk-pixbuf, linux, linux-aws, linux-aws-5.15, linux-gcp, linux-gcp-5.15, linux-gke,
linux-gkeop, linux-ibm, linux-ibm-5.15, linux-intel-iotg,
linux-intel-iotg-5.15, linux-kvm, linux-lowlatency,
linux-lowlatency-hwe-5.15, linux-nvidia, linux-nvidia-tegra,
linux-nvidia-tegra-igx, linux-oracle, linux-oracle-5.15, linux-raspi,
linux-xilinx-zynqmp, linux-aws-6.8, linux-gcp-6.8, linux-hwe-6.8, linux-ibm-6.8,
linux-lowlatency-hwe-6.8, linux-fips, linux-aws-fips, linux-gcp-fips, linux-oracle, linux-oracle-6.17, linux-raspi, linux-realtime, openssl, and squid).
Post Syndicated from Ed Montgomery original https://www.rapid7.com/blog/post/pt-whats-new-rapid7-products-services-q1-2026
If product releases had a runway moment, Q1 at Rapid7 would’ve walked out in Cloud Dancer; crisp, confident, and quietly powerful, before breaking into a full gallop in the Year of the Horse. At Rapid7, our first-quarter launches combined velocity with refinement: meaningful enhancements designed to move security teams faster without adding complexity. Let’s cover off the key launches, one by one.
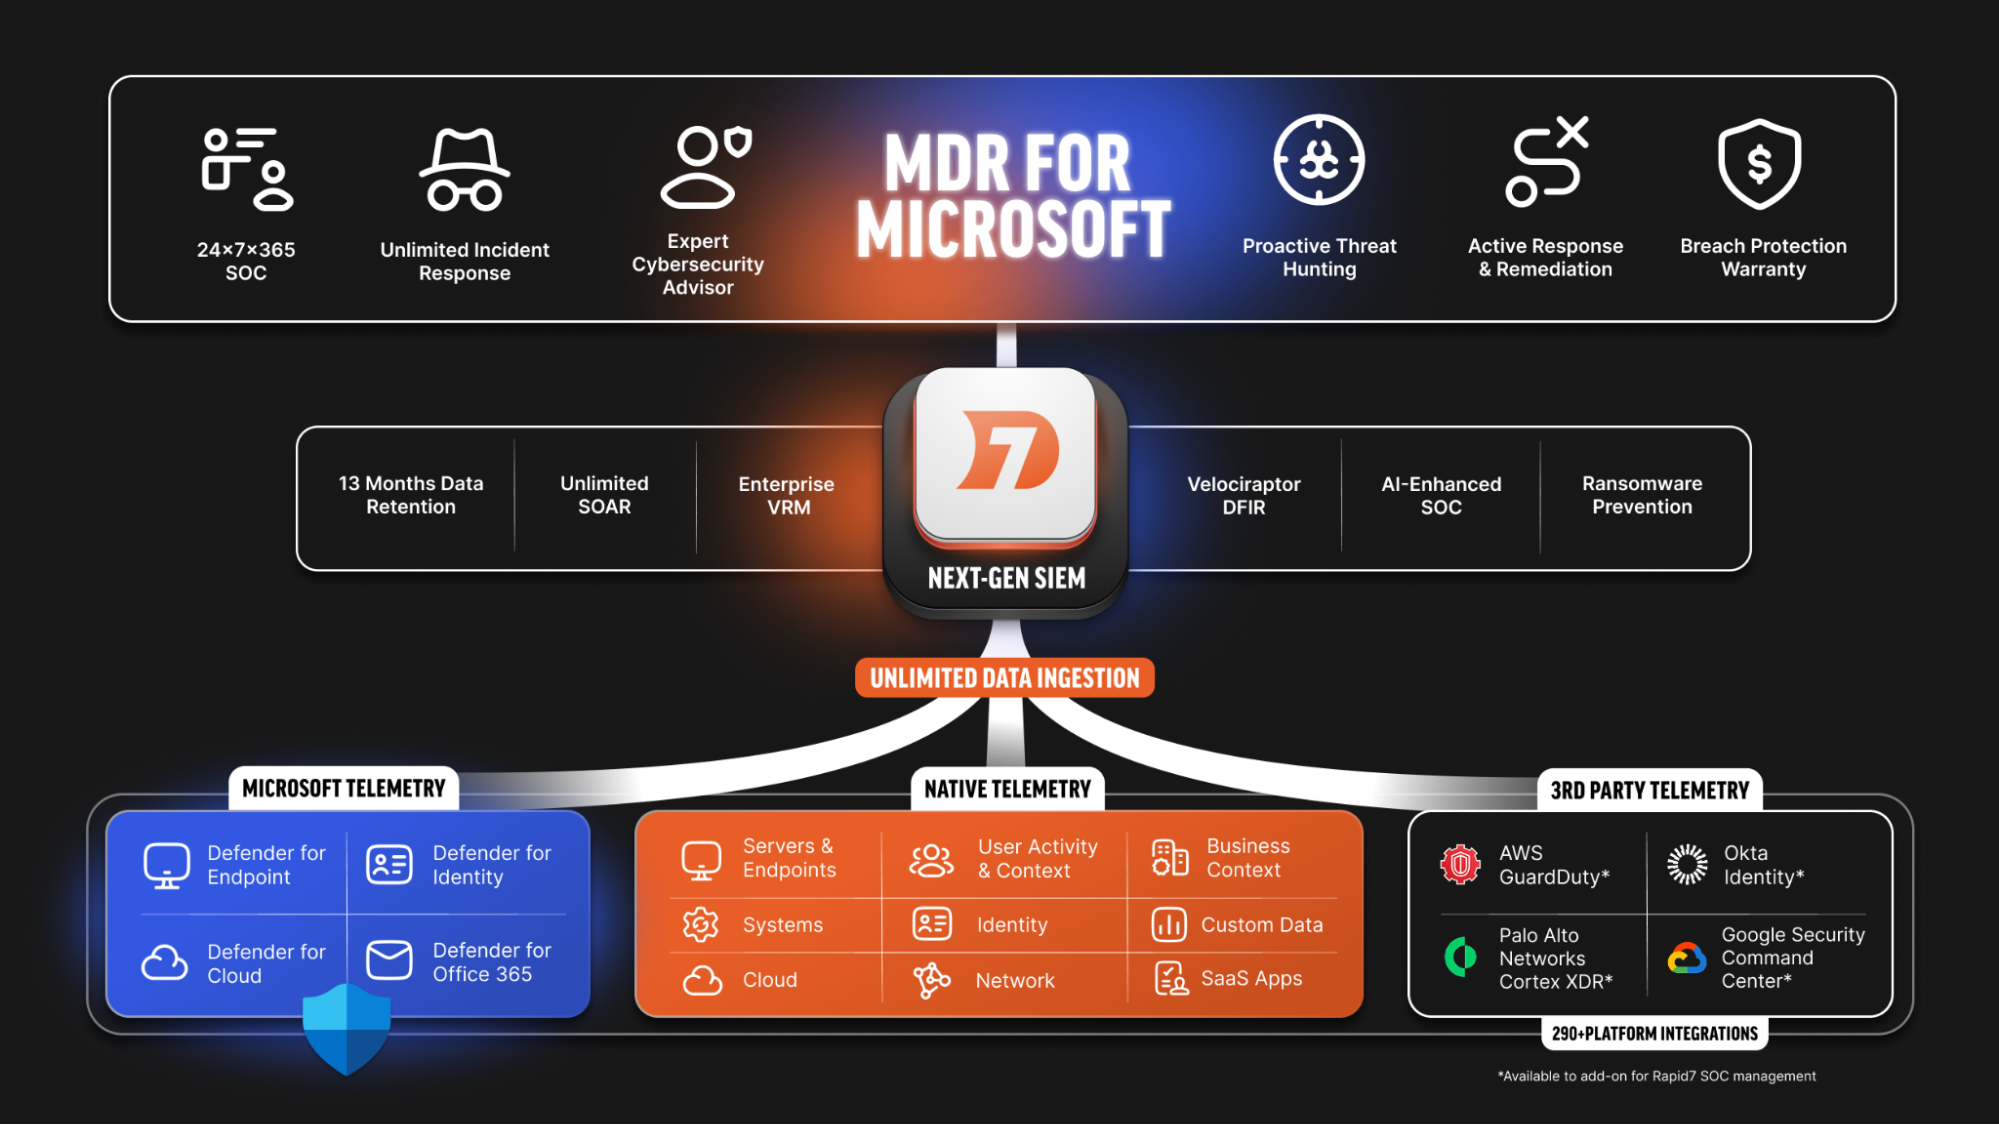
Getting more value from the tools you already have is an objective shared by all of us. For many of you, that translates to achieving greater security operations outcomes and resilience from your Microsoft technology. With MDR for Microsoft, organizations correlate their Microsoft, Rapid7, and third-party telemetry with prioritized risk context so the service can anticipate attacks before they start.
AI-powered triage and investigations – backed by unlimited incident response that ensures threats are fully eradicated – delivers certainty in an uncertain attack environment. Dedicated advisory provides strategic recommendations and program hardening guidance that drives long-term security resilience. Customers ultimately experience security operations excellence and achieve stronger outcomes from their existing Microsoft foundation.
Read the blog to learn more.
The acquisition of Kenzo Security marks another step forward for the Rapid7 Command Platform and Rapid7’s vision for preemptive, AI-powered security operations. In an environment where most security teams are forced to leave large volumes of alerts uninvestigated, Kenzo’s agentic AI capabilities are expected to help accelerate Rapid7 from AI-assisted workflows toward AI-driven, machine-speed operations. Designed around specialized AI agents that work together across security operations tasks, this technology has the potential to reduce manual strain, broaden investigative coverage, and deliver more consistent, precise outcomes.
An average Kenzo customer reported a 94% reduction in investigation time, and their alert coverage increased from 12% to 100%. As these capabilities are brought into MDR, Managed Threat Complete, InsightIDR, and Incident Command, customers will benefit from a stronger, more scalable approach to cyber defense.
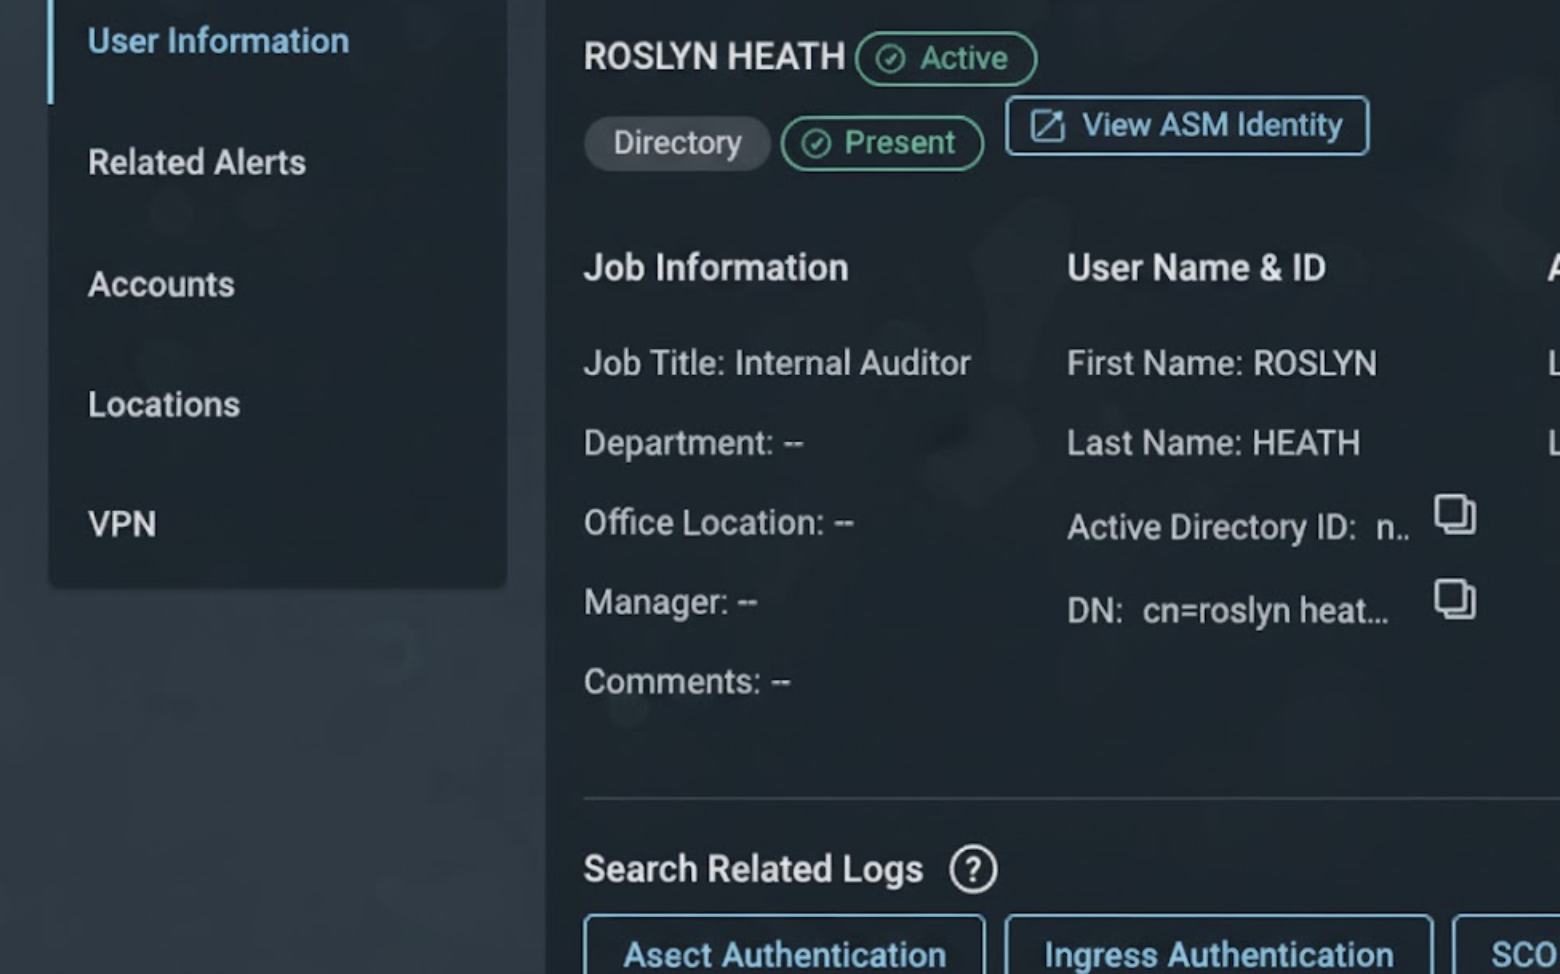
Connecting user activity to full identity context is critical for faster, more confident investigations. With User to Identity mapping in Incident Command, analysts can seamlessly link SIEM users to their corresponding identity profiles, gaining instant visibility into MFA status, account posture, and group memberships. By unifying detection and exposure data, teams eliminate manual reconciliation and close visibility gaps across the identity attack surface. This enables faster triage, deeper insight into user risk, and a complete, connected view of identity-driven threats.
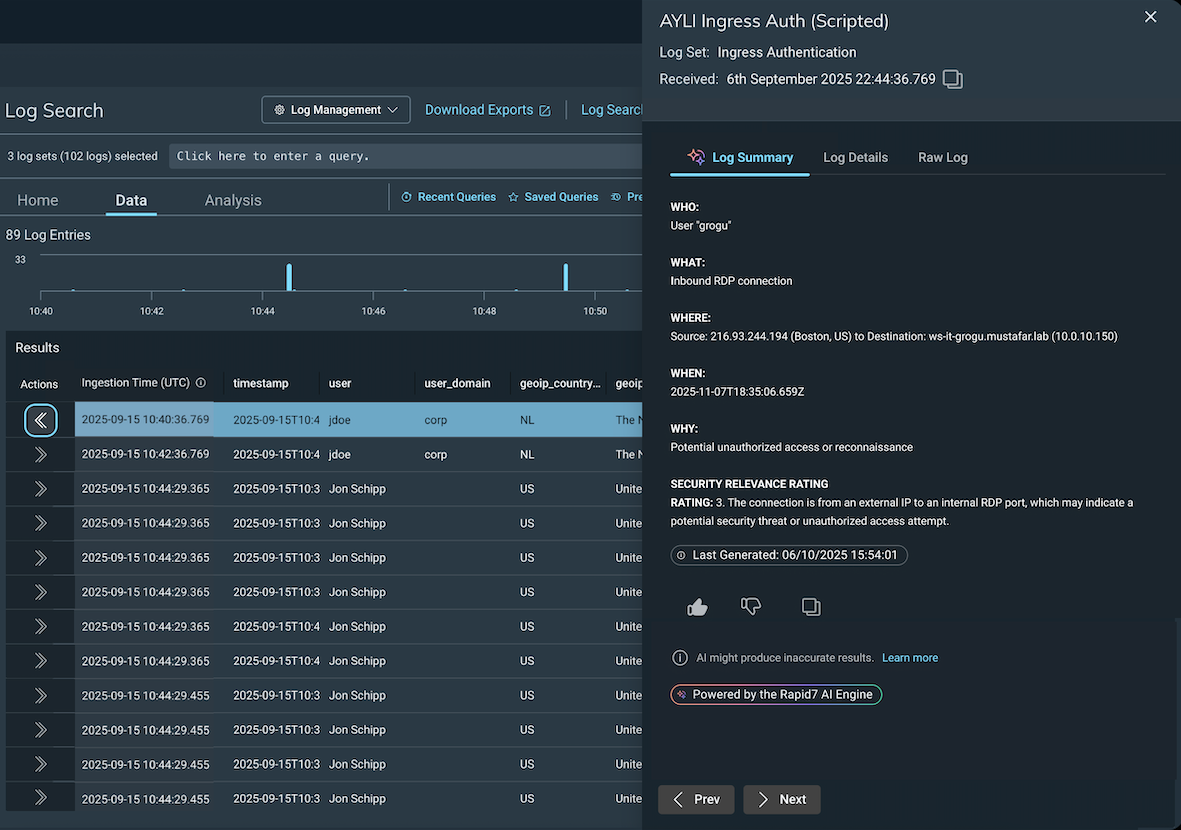
AI-powered Log Entry Summary brings instant clarity to even the most complex log data. By translating raw log lines into a simple “who, what, when, where, and why” framework, analysts can quickly uncover insights without needing to interpret vendor-specific syntax or business logic. This removes the cognitive burden from investigations and hunts, allowing teams to spot threats faster across all data sources. Teams benefit from accelerated triage, more efficient investigations, and smarter decisions driven by clear, actionable context.
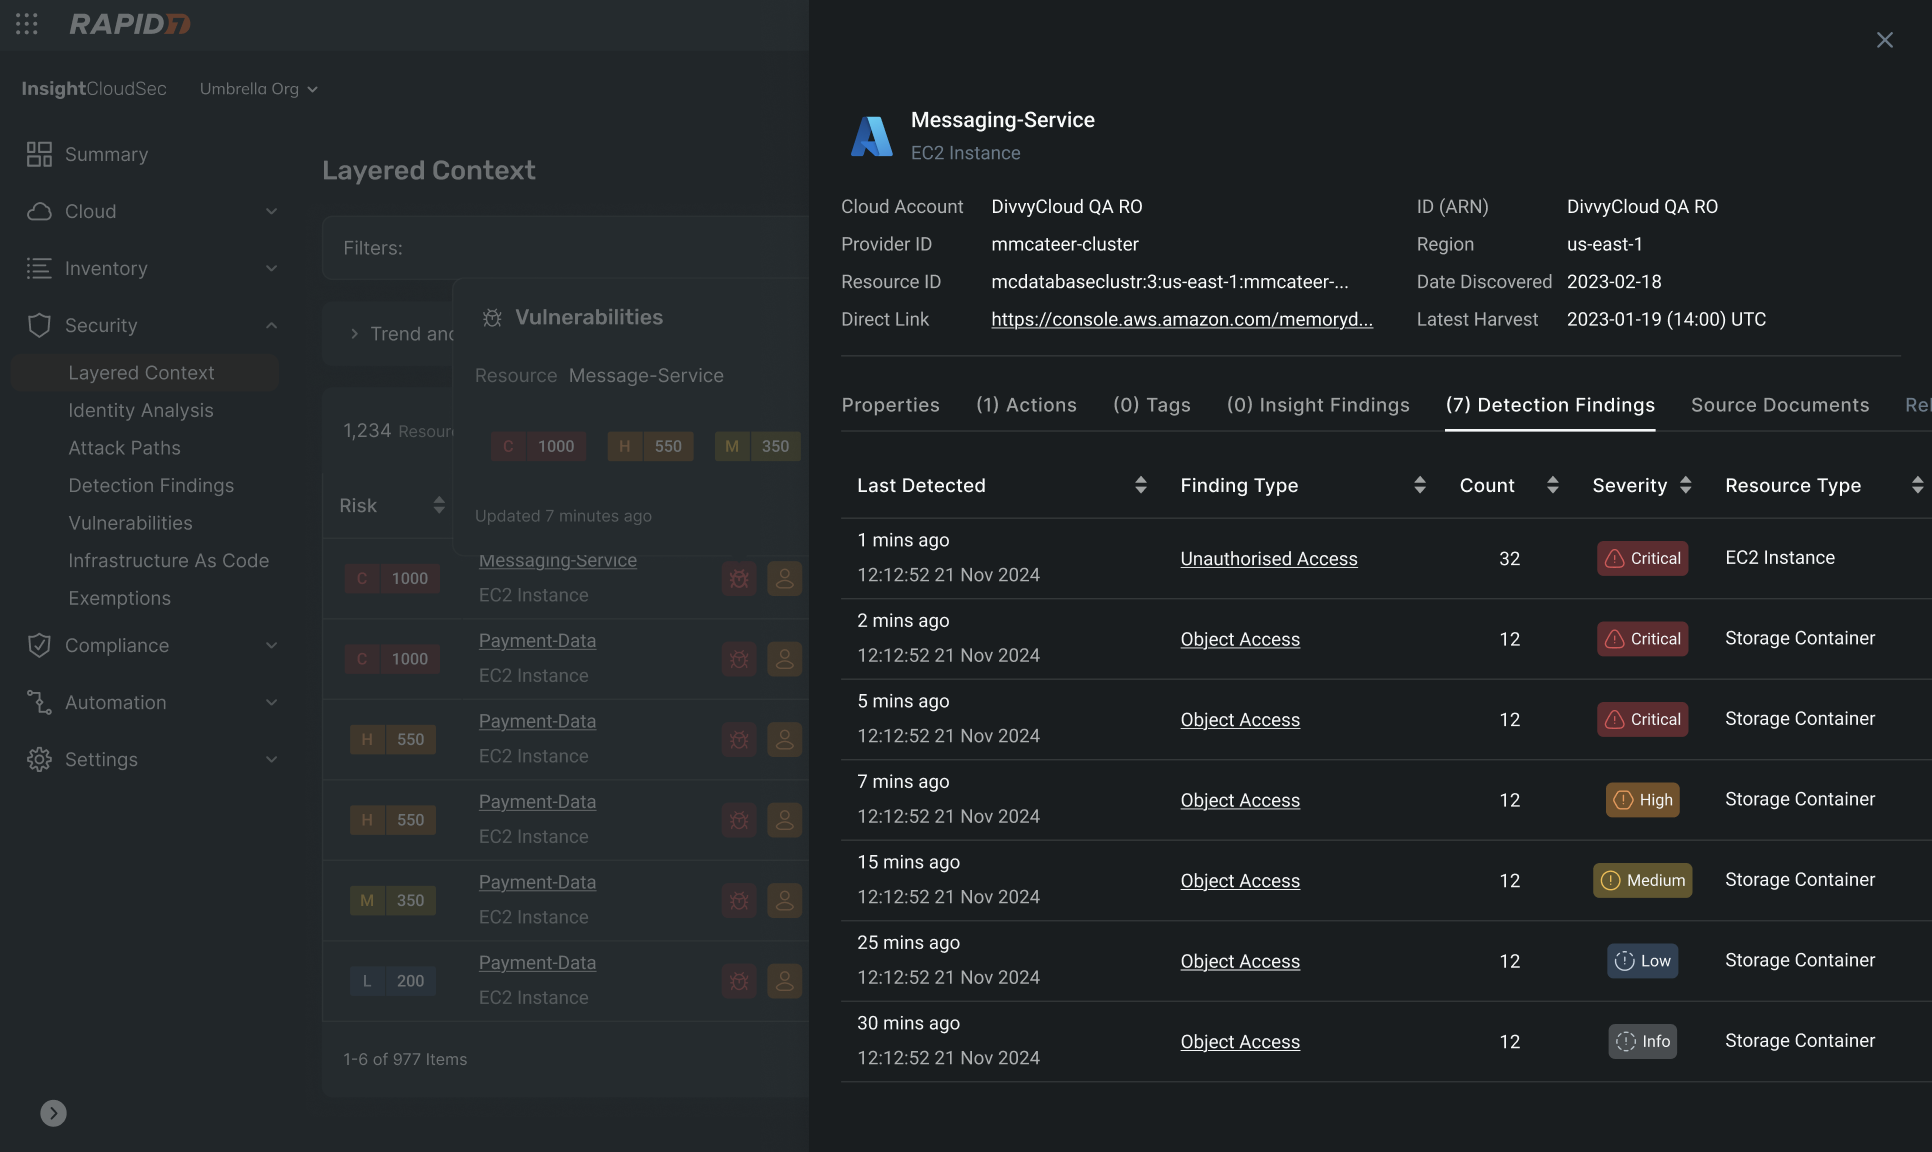
Earlier this year, we made a significant announcement that Rapid7 had partnered with ARMO to add AI-powered cloud application detection and response (CADR) – or cloud runtime security – to our cloud security portfolio. We are thrilled to announce that these capabilities are now integrated with Rapid7 Exposure Command Ultimate. For our customers, this milestone represents our ability to deliver on the promise of a complete cloud-native application protection platform (CNAPP) that helps security teams preemptively identify and proactively thwart attacks. If you’re interested in learning more about this latest innovation to our cloud security portfolio, reach out to one of our account executives.
Understanding which remediations to prioritize is only part of the process, teams also need asset-level detail to act. Top Remediations Report adds that context in Remediation Hub, with customizable filters, shared visibility across teams, and automated scheduling for recurring delivery to key stakeholders in CSV, HTML, or PDF. The result is faster coordination, clearer ownership, and quicker remediation progress.
We understand that organizations need to customize reporting for various stakeholders and levels across their business to drive effective vulnerability remediation and communicate security posture. One of the ways that organizations address this need is through our powerful cloud-based API, which enables teams to extract and export large amounts of security data into external tools like Tableau or PowerBI. Customers can export security data at scale, including assets, vulnerabilities, remediations and agent-based policy data, resulting in more flexible reporting and querying.
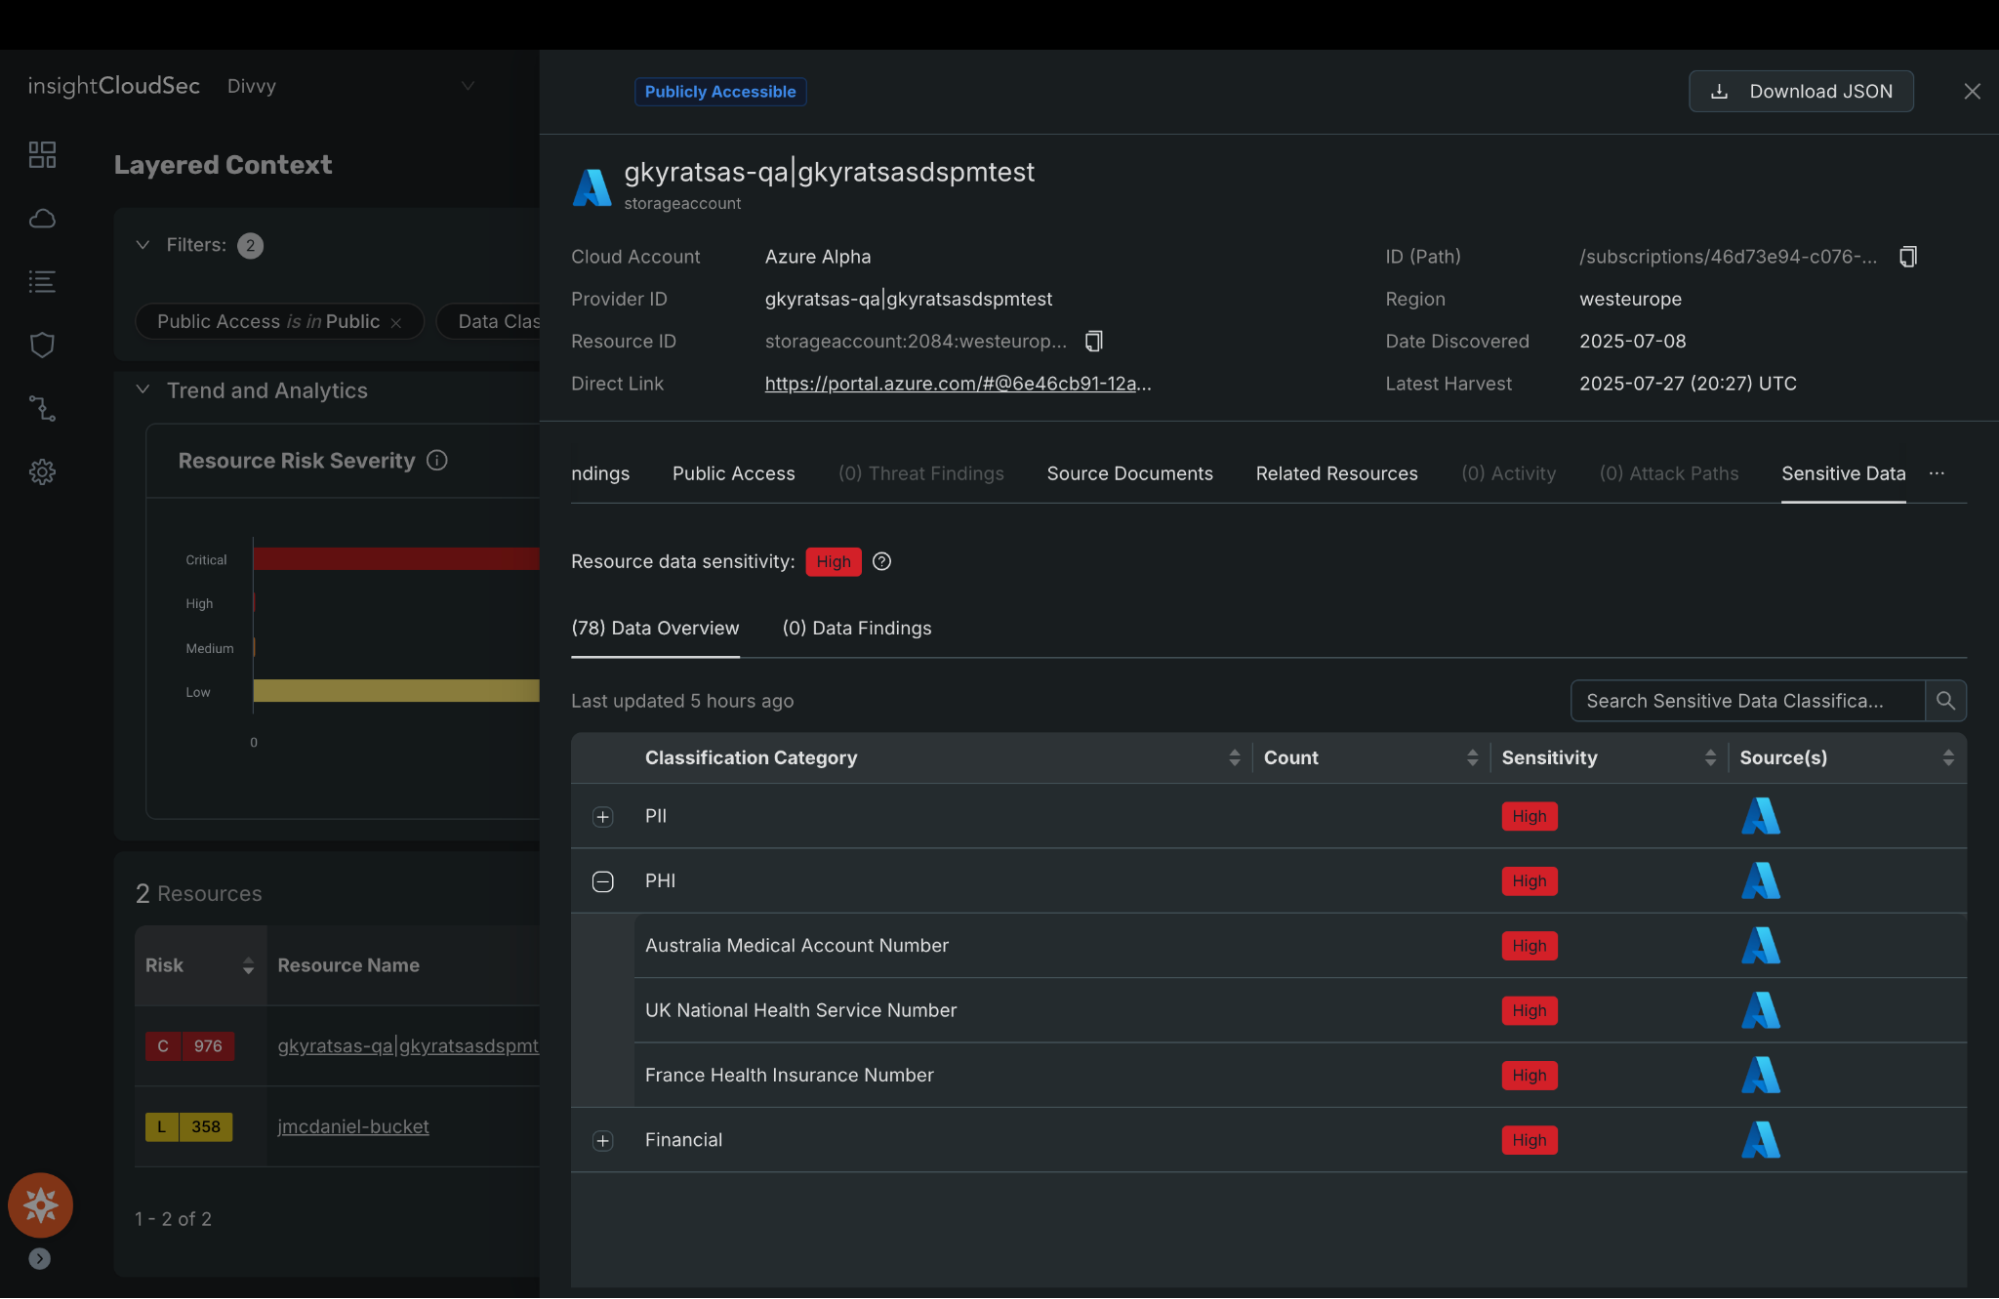
Understanding which exposures threaten sensitive data is difficult when data security and exposure insights live in separate tools. A partnership between Rapid7 and Symmetry Systems brings those perspectives together on Exposure Command, aligning sensitive data intelligence with real attacker reachability. DSPM capabilities discover sensitive data and map identity access, helping teams prioritize remediation based on breach impact.
Read the blog to learn how aligning data and exposure reduces breach risk.
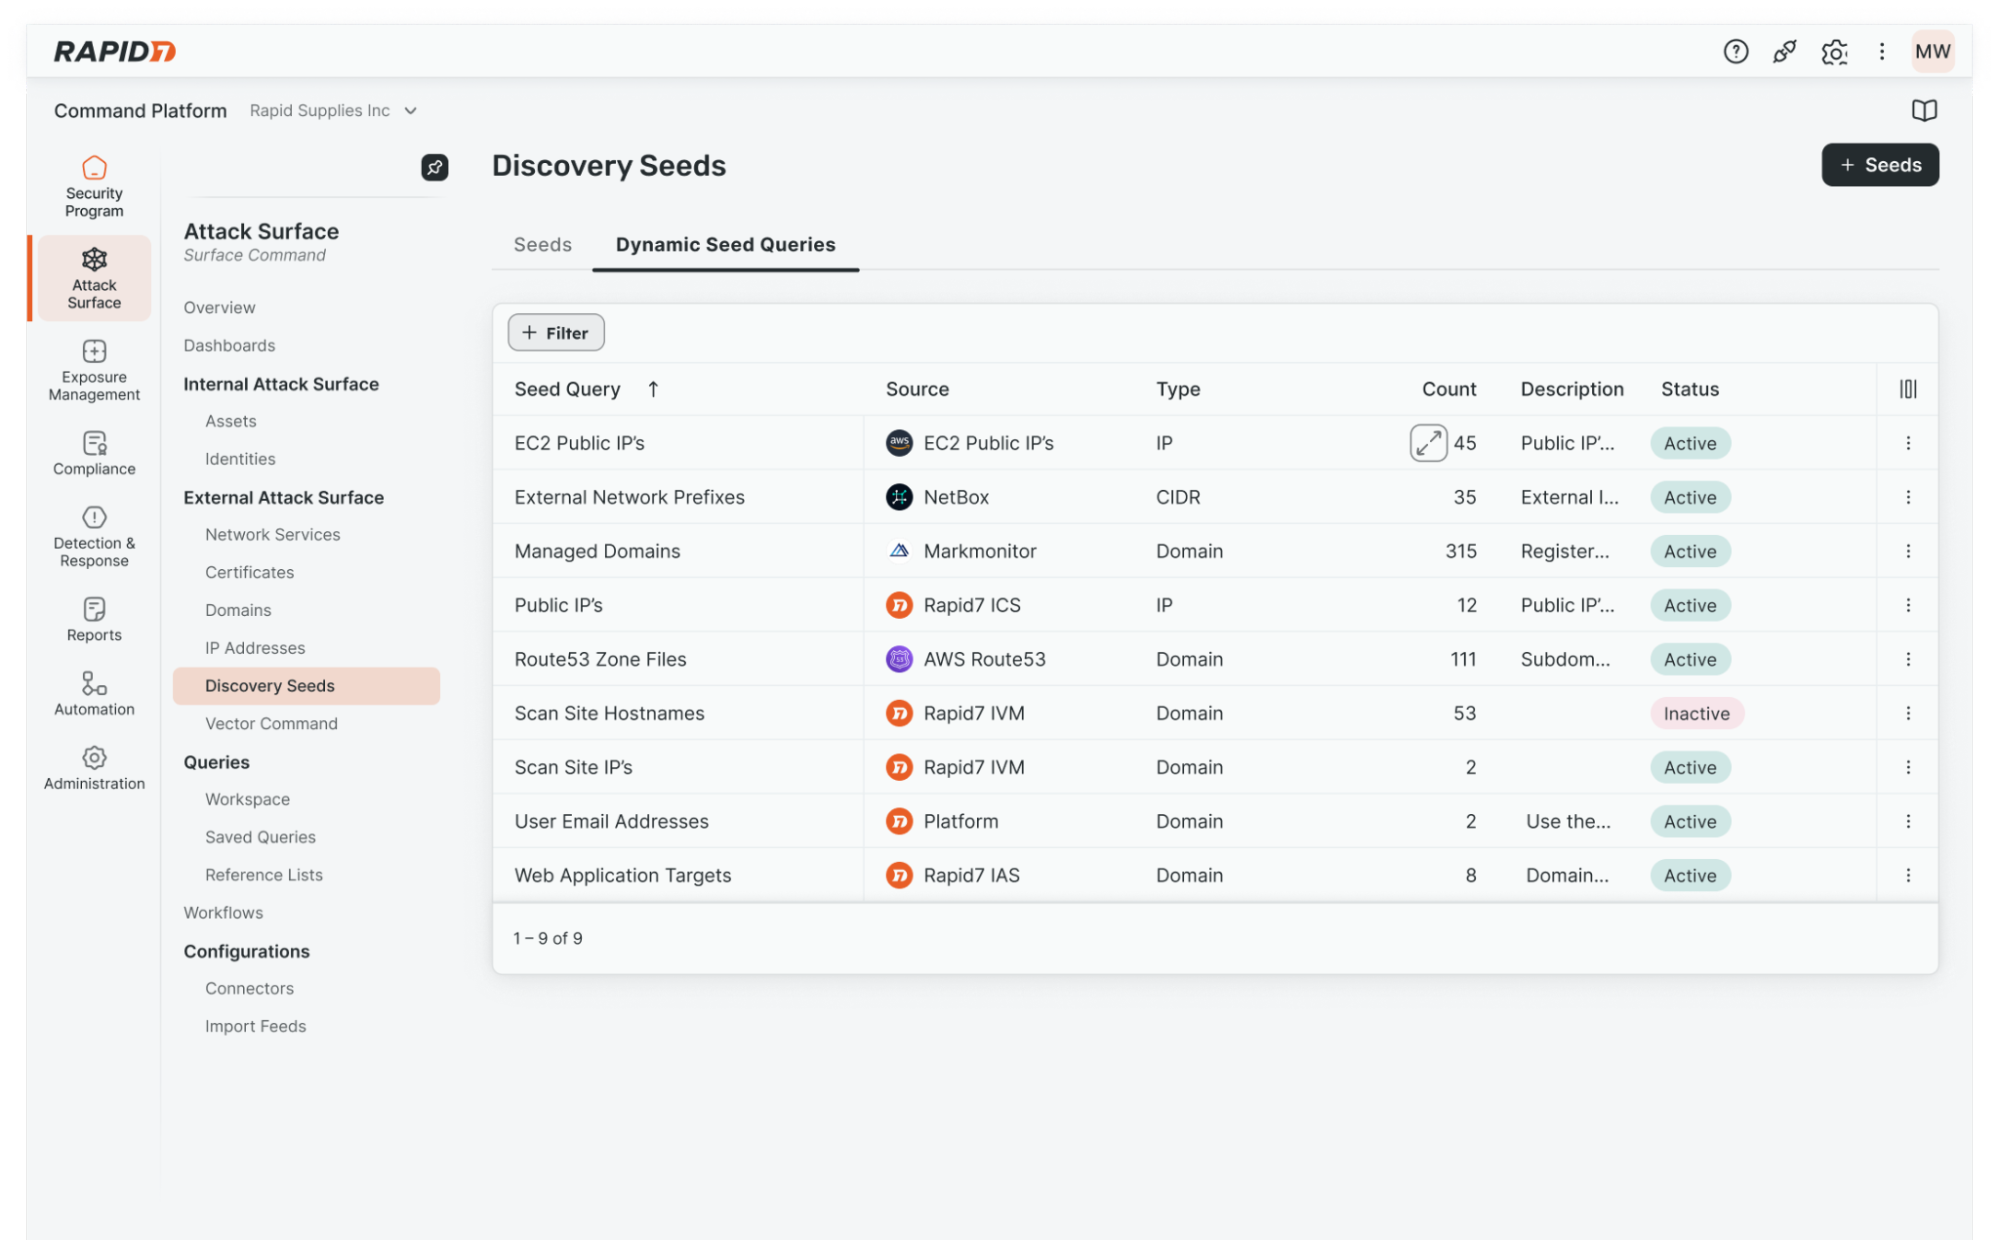
Your attack surface doesn’t stand still, and point-in-time visibility can leave teams chasing what’s already changed. Dynamic EASM Discovery helps Surface Command automatically identify and track changes across the external attack surface by ingesting domain and IP data from across the environment. The result is more current visibility, fewer blind spots, and stronger confidence that teams are prioritizing and validating the exposures that matter most.
Read the blog to see how Dynamic EASM Discovery helps teams keep pace with a changing attack surface.
We’re excited to introduce a centralized way to programmatically access data across all managed tenants with new multi-tenant API keys. For organizations managing multiple environments, tenants, or customers, integrating with each one individually has traditionally required significant manual effort, creating, maintaining, and rotating separate API keys for every tenant. This not only slows down development but also increases operational overhead and the risk of inconsistency.
With this new capability, you can build a single integration that seamlessly “loops” through tenants automatically, enabling consistent data access and streamlined workflows at scale. Whether you’re aggregating data for reporting, powering automation, or integrating with third-party tools, multi-tenant API keys simplify the process and reduce complexity, freeing up your teams to focus on higher-value tasks instead of repetitive configuration. Read all about it in our blog.
This quarter Rapid7 Labs continued to deliver critical insights into the evolving threat landscape, uncovering how attackers are adapting their tactics – from stealthy, long-term intrusions to increasingly targeted and data-driven attacks. Our latest research reports highlight the growing complexity of modern threats and the real-world risks facing organizations today. Explore the findings below to better understand what’s changing and what it means for your security strategy.
BPFdoor in Telecom Networks: Sleeper Cells in the Backbone: Rapid7 uncovered a long-running espionage campaign in which a China-nexus threat actor, Red Menshen, embedded stealthy “sleeper cells” inside global telecommunications networks using the BPFdoor backdoor. Operating at the Linux kernel level, this malware enables persistent, hard-to-detect access without typical network signals, allowing attackers to monitor communications, subscriber data, and critical infrastructure over time. The research highlights a shift from opportunistic attacks to deliberate, long-term pre-positioning inside core systems that underpin global connectivity, raising national-level risk.
2026 Global Threat Landscape Report: The latest report from Rapid7 Labs delivers an in-depth analysis of global adversary behavior, drawing on telemetry from Rapid7 MDR investigations, vulnerability intelligence, and frontline incident response. This year’s findings highlight a rapidly evolving threat environment, marked by the collapse of the window between vulnerability disclosure and exploitation, the continued industrialization of ransomware operations, and the acceleration of modern attacks through the use of AI.
Executives’ Digital Footprints Threat Report: Today, 60% of an executive’s digital risk exposure is retrievable through surface web searches, including public records, professional history, and social media activity — all of which can be weaponized for highly targeted attacks. The Executive Digital Footprints Threat Report from Rapid7 Labs details how these executive digital footprints are an often overlooked threat vector that can be exploited, posing risks to the executive, their families, and organizations.
Last month, Rapid7 uncovered the Chrysalis backdoor, a sophisticated supply chain attack that leveraged the Notepad++ update mechanism to selectively target organizations with a stealthy, persistent backdoor. This discovery highlights the growing risk of trusted software being weaponized and the real-world impact of advanced, targeted campaigns that can evade traditional defenses, reinforcing the importance of continuous monitoring and validating third-party software behavior in today’s threat landscape. Learn more about the Chrysalis backdoor here, and see more details on its impact and what you can do next here.
Rapid7 is actively monitoring cyber threat activity related to the Iran conflict, providing support for our customers and the cybersecurity community. Review observed activity, official advisories, and recommended defensive actions here.
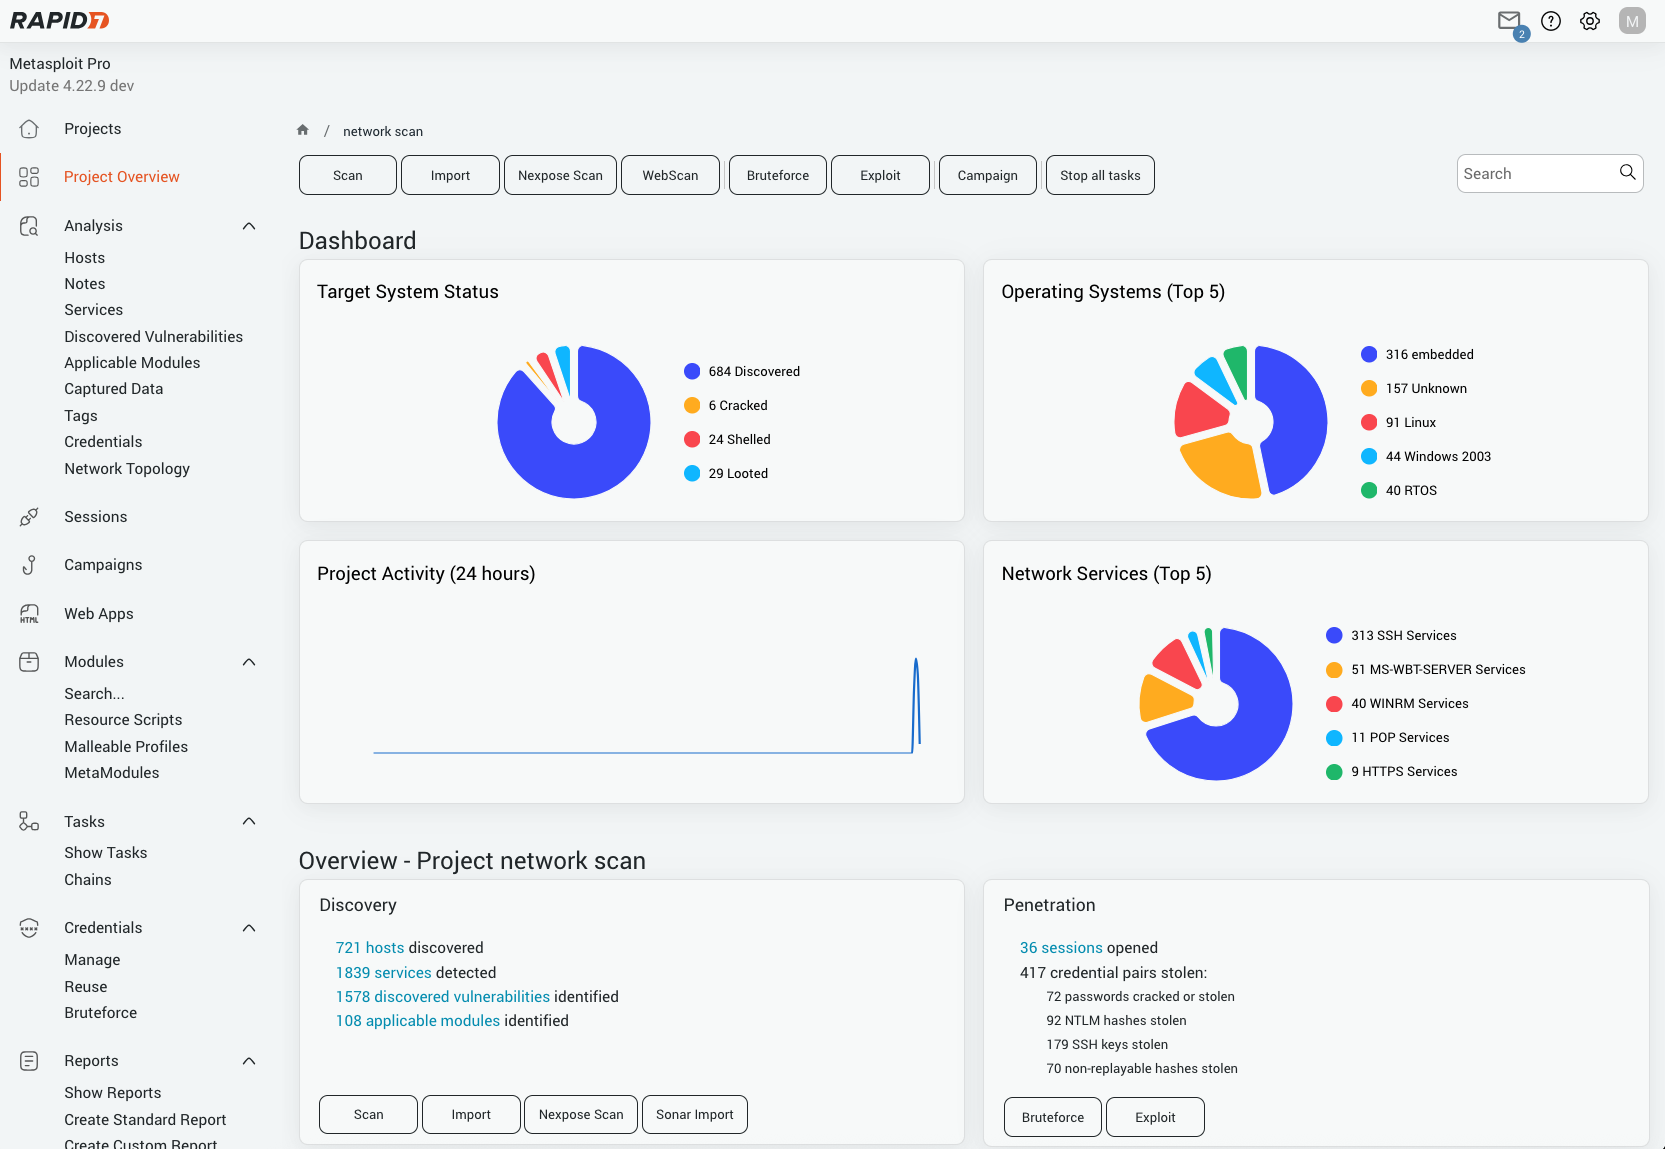
We’re excited to announce the launch of Metasploit Pro 5.0.0, a major evolution in red-team and penetration testing. Built to address today’s dynamic threat landscape, this release delivers a significantly improved UI, usability, validation, and workflow improvements that empower security teams to validate vulnerabilities faster and more effectively. Learn more in our blog post here.
The innovation doesn’t stop here. We have a strong pipeline of product enhancements and new capabilities rolling out all year long. Be sure to follow our blog and release notes to see how Rapid7 continues to advance our platform and deliver greater value.
Post Syndicated from Sophie Ashford original https://www.raspberrypi.org/blog/many-paths-into-mentoring-building-inclusive-code-clubs-in-glasgow/
Across Glasgow’s libraries, Code Clubs are opening doors for young people to explore creativity, problem-solving, and confidence through coding. Behind many of these sessions is Claire Quigley, who supports volunteers and helps Code Clubs thrive in community spaces across the city.
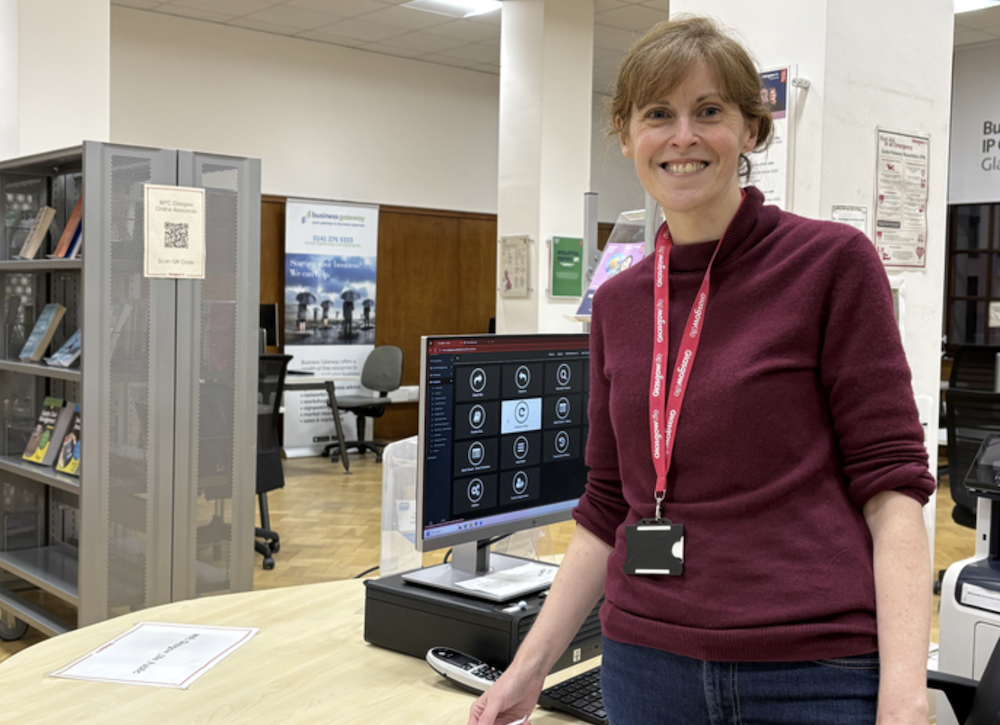
Claire’s story challenges the idea that there is only one route into technology or mentoring. With a background in computer science and a passion for teaching, she now helps create welcoming, inclusive environments where young people — and volunteers — from a wide range of backgrounds can belong.
Claire’s Code Club journey began long before she worked in libraries. With a degree and PhD in computer science, she spent time in academia before finding her way to community-based learning and volunteering. Teaching runs in her family, and sharing knowledge has always brought her joy. That’s why, after being introduced to CoderDojo (part of the Code Club community) through a friend, Claire began volunteering at club sessions.
“I had always intended to work in academia but, working as a postdoc for a couple of years, realised it wasn’t what I wanted to do long term. CoderDojo sessions gave me and the other volunteers a chance to look at more adventurous coding topics, without the constraints of curriculum and the time-pressure that teachers have to contend with.
“We were also able to engage with children and young people who were struggling with the formal education environment for a variety of reasons. Doing well at something they enjoyed increased their confidence and was often a factor in helping them become more engaged at school.”
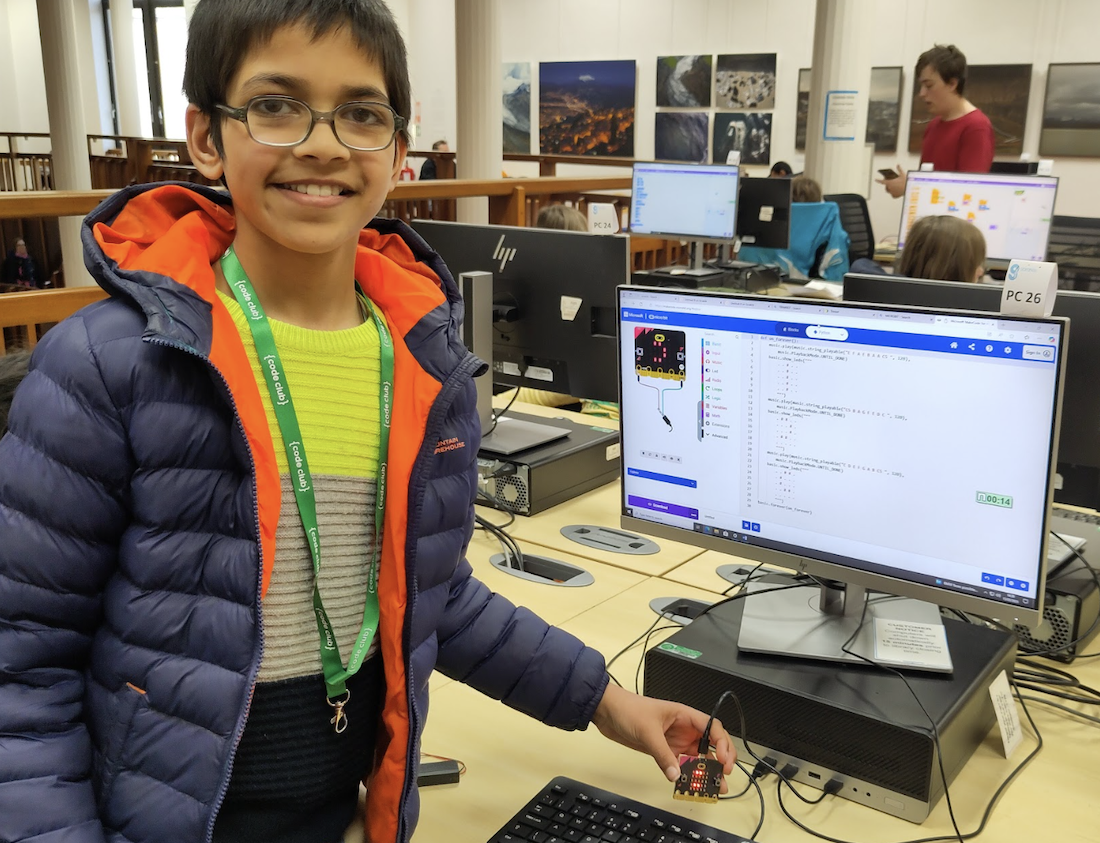
Becoming a Code Club volunteer eventually led Claire to her current role coordinating Code Clubs across Glasgow Life venues, including Mitchell Library, Gorbals, Drumchapel, and beyond.
“Working with Glasgow Life colleagues across libraries, communities and museums has given me the chance to connect with children, young people and adults in a non-threatening environment. Mixing coding with mediaeval manuscripts, wearable tech, poetry or electronic music has allowed people to approach a topic they hadn’t considered interesting or understandable and make some really original and fun things.”
Stepping into one of Claire’s Code Club sessions, you’ll find a mix of focus, laughter, and creative chaos. Young people gather around laptops in library spaces to build games and animations in Scratch, experiment with micro:bits, and help each other solve problems as they go.
Sessions vary by location and age group. Some run weekly, others every two weeks, and each has its own character — from younger children discovering coding for the first time to teenagers returning with ambitious ideas they want to bring to life.
“The clubs are quite varied, depending on location, size and the personality mix of the coders and volunteers. Some clubs are quieter, while others are very lively! Scratch features prominently in most clubs. The children really enjoy the way it allows them to bring in topics they’re interested in, design their own characters, or build games inspired by other games they’ve played.”
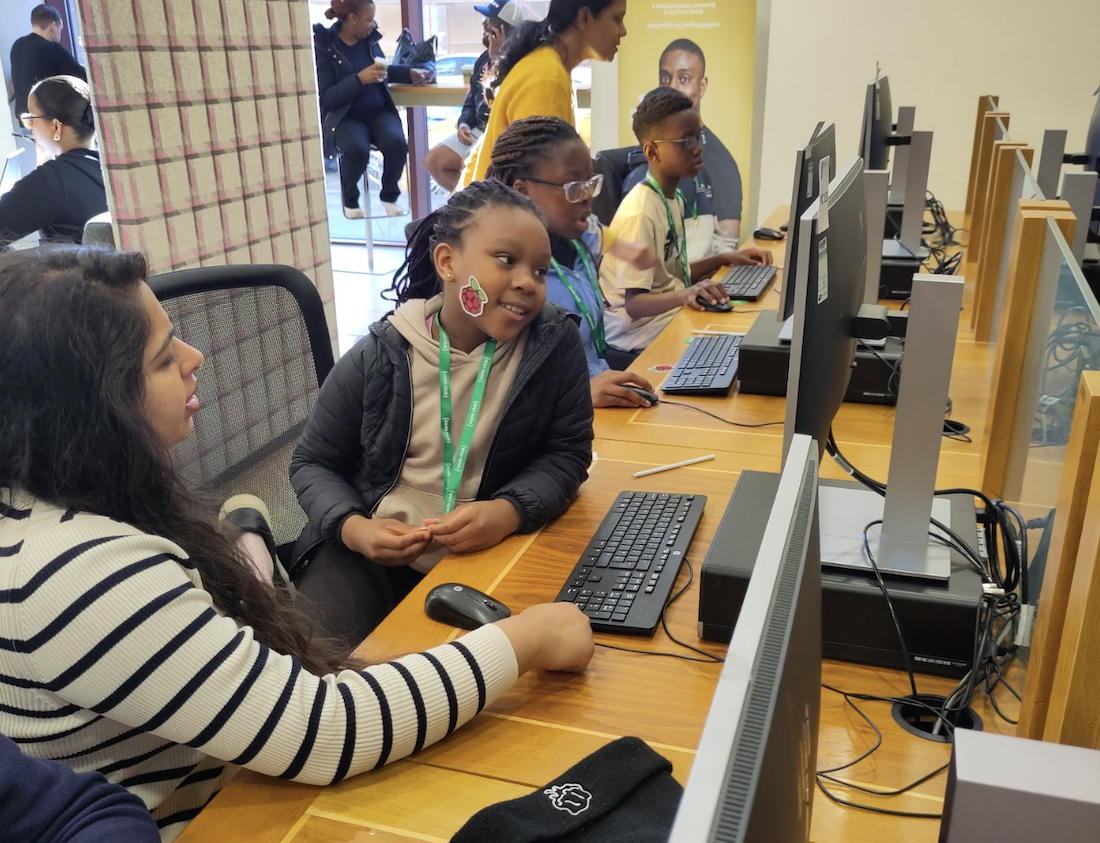
For Claire, these sessions are about more than learning to code. They’re spaces where young people practise problem-solving, learn to ask for help, and gain confidence in sharing their ideas.
“Some coders come with a friend or have made friends at the club. So there are often children working together on a project, chatting to each other about what they’re working on, or showing each other how to do something.”
Inclusion is core to Claire’s approach. From running all-girls sessions to supporting volunteers and young people with neurodivergence and other additional needs, her focus is on creating spaces where everyone feels welcome.
“One young coder who spends a lot of time in his local library after school, but can be a bit boisterous, agreed to come and join the club. Initially a bit hesitant, he soon displayed a real talent for solving coding puzzles.
“He was particularly proud when, encouraged to try the challenge level rather than skipping past it, he solved it quickly. We printed a Code Club ‘Problem-solving Champion’ certificate for him and he carefully folded it up to take home.“
Claire has seen firsthand how confidence can grow when people are given time, patience, and encouragement.
That sense of belonging doesn’t stop with young people — it extends to the volunteers who help make these spaces possible. For some volunteers, involvement in Code Club has been a stepping stone to employment, new skills, or a stronger sense of belonging.
Like many community programmes, Code Clubs in Glasgow were disrupted by the pandemic. It made one thing clear: clubs only work when volunteers are willing and supported to run them. With fewer library staff available to anchor sessions, rebuilding the clubs meant casting a wider net for volunteers. As a result, volunteers arrived with more diverse life experiences, ways of thinking, and approaches to problem-solving, which enriched the sessions and created more inclusive learning environments for young people.
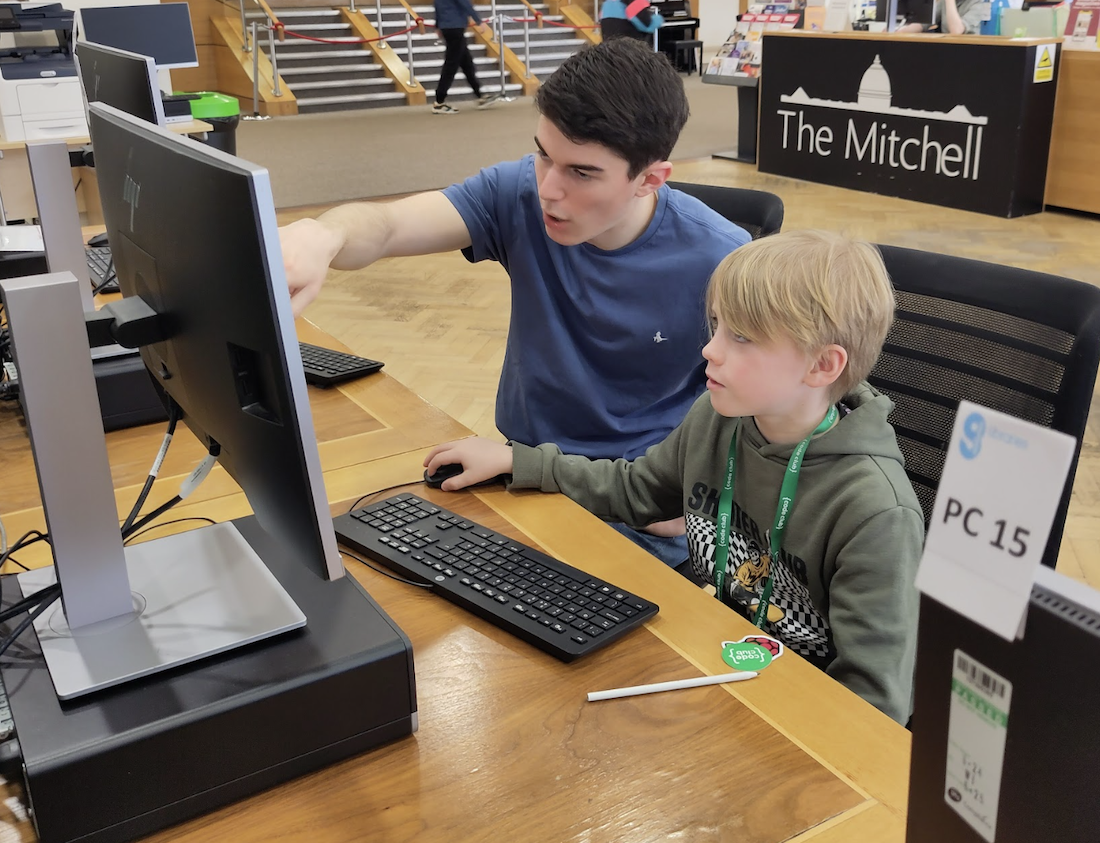
“I recruit mainly through the Glasgow Life volunteering website. I also advertise through STEM Ambassadors, via my contacts in local universities, colleges and tech companies, in the newsletter my colleague sends to students in the Glasgow Code Learning programme, and by putting up posters in libraries.
“I’m really keen to try and get a mixture of qualities in a team. I try to ensure at least one person is a confident programmer, who can help with trickier bugs and more advanced topics. However, I’m also keen to have volunteers who may not have so much of a technical background but are good at chatting to children and helping create a real sense of it being a club.“
One of the most important messages Claire wants to share is that there is no single type of Code Club volunteer. Students, career-changers, refugees, people returning to work, and neurodivergent people all bring valuable perspectives. While technical skills are helpful, Claire believes empathy, curiosity, and willingness to learn alongside young people are just as important.
“Finding out how to do something by searching online, asking other coders and the mentors is part of the code club experience (and the experience of being a professional programmer!) The main thing is not to be afraid to admit you don’t know something. Although this can be alarming at first, I’ve found the coders are happy to be told that I’ll look at it over the next week and report back. And that they should do the same so we can compare notes. And if they know how to do something that you don’t, they absolutely love explaining it to you!“
We asked Claire what she would say to someone who doesn’t see themselves as ‘technical enough’ but is curious about getting involved:
“The majority of library staff didn’t have any background in programming. They are simply happy to learn as they go along and help the children make their ideas come to life. In fact, one of these ‘non-technical’ staff ran a very popular and successful club and supported a team of coders to develop a project that [was chosen as a judges’ favourite] at Coolest Projects.”
As Code Clubs continue to grow and adapt, Claire hopes to see even more people step forward, especially those who might not immediately picture themselves in a mentoring or volunteering role.
By keeping Code Clubs rooted in libraries and community spaces, it is possible to reach people across a wide range of backgrounds and circumstances.
Claire’s story is a reminder that community impact is built by people who care and that supporting young people with coding is about far more than technology alone. It’s about confidence, connection, and opening doors.
For anyone curious about supporting young people with coding, there are many ways to get involved. You don’t need to be an expert, as mentors support young people by encouraging curiosity, helping build confidence, and learning alongside them. If you’d like to find out more about what mentoring looks like and the different ways you can contribute, visit the Code Club mentor page to explore guidance, training, and next steps.
The post Many paths into mentoring: Building inclusive Code Clubs in Glasgow appeared first on Raspberry Pi Foundation.
Post Syndicated from Matt Granger original https://www.youtube.com/watch?v=Kesu6HcSB04
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2026/04/on-microsofts-lousy-cloud-security.html
ProPublica has a scoop:
In late 2024, the federal government’s cybersecurity evaluators rendered a troubling verdict on one of Microsoft’s biggest cloud computing offerings.
The tech giant’s “lack of proper detailed security documentation” left reviewers with a “lack of confidence in assessing the system’s overall security posture,” according to an internal government report reviewed by ProPublica.
Or, as one member of the team put it: “The package is a pile of shit.”
For years, reviewers said, Microsoft had tried and failed to fully explain how it protects sensitive information in the cloud as it hops from server to server across the digital terrain. Given that and other unknowns, government experts couldn’t vouch for the technology’s security.
[…]
The federal government could be further exposed if it couldn’t verify the cybersecurity of Microsoft’s Government Community Cloud High, a suite of cloud-based services intended to safeguard some of the nation’s most sensitive information.
Yet, in a highly unusual move that still reverberates across Washington, the Federal Risk and Authorization Management Program, or FedRAMP, authorized the product anyway, bestowing what amounts to the federal government’s cybersecurity seal of approval. FedRAMP’s ruling—which included a kind of “buyer beware” notice to any federal agency considering GCC High—helped Microsoft expand a government business empire worth billions of dollars.
Post Syndicated from The Atlantic original https://www.youtube.com/watch?v=v0OhA8GDvlk