Post Syndicated from Matt Granger original https://www.youtube.com/shorts/IZmEL8CCHxA
Windows Monitoring with Zabbix
Post Syndicated from Arturs Lontons original https://blog.zabbix.com/windows-monitoring-with-zabbix/33053/
Windows environments provide a variety of approaches for monitoring both on the OS and the application level. The article will cover utilizing Zabbix agent on Windows to collect and discover OS and application level metrics from a variety of Windows-supported sources.
Deploying Zabbix agent on Windows
Zabbix agent can be deployed either by downloading the official MSI packages or by installing the Zabbix agent from binary files. Both Zabbix agent and Zabbix agent 2 are available to install via these methods. Generally speaking, Zabbix agent 2 is a more feature-rich version than the regular Zabbix agent. On the other hand, if you do encounter any compatibility issues with Zabbix agent 2 – the classic Zabbix agent can be used instead.
During the MSI install the following Zabbix agent configuration parameters can be defined:
- Zabbix server address
- Zabbix agent PSK encryption settings
- Direction of the connection (Active/Passive checks)
- Optional install of Zabbix sender and Zabbix get tools
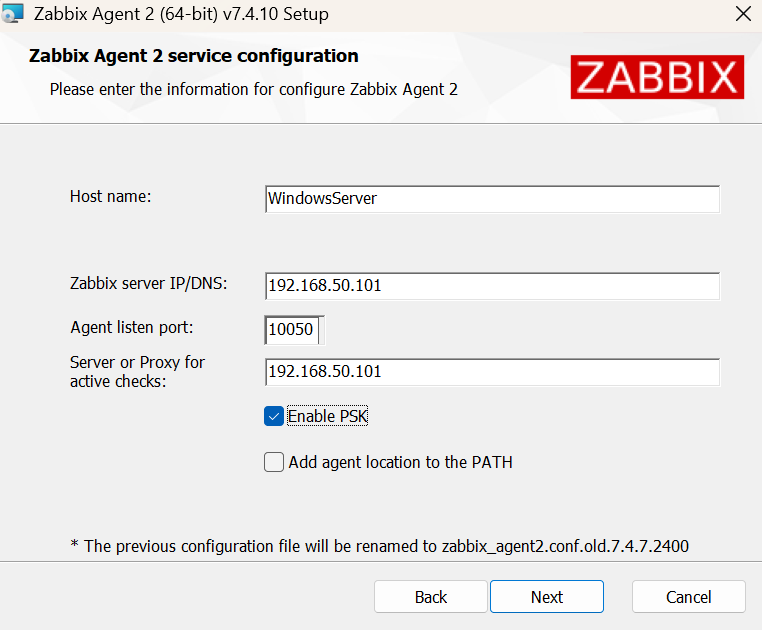
Installing Zabbix agent from binary file is also a fast and simple process:
- Download the Zabbix agent binary files
- Adjust the Zabbix agent configuration file to fit your requirements
- Run the agent binary file with the —install command
- Use the –config command to point the Zabbix agent at the agent configuration file
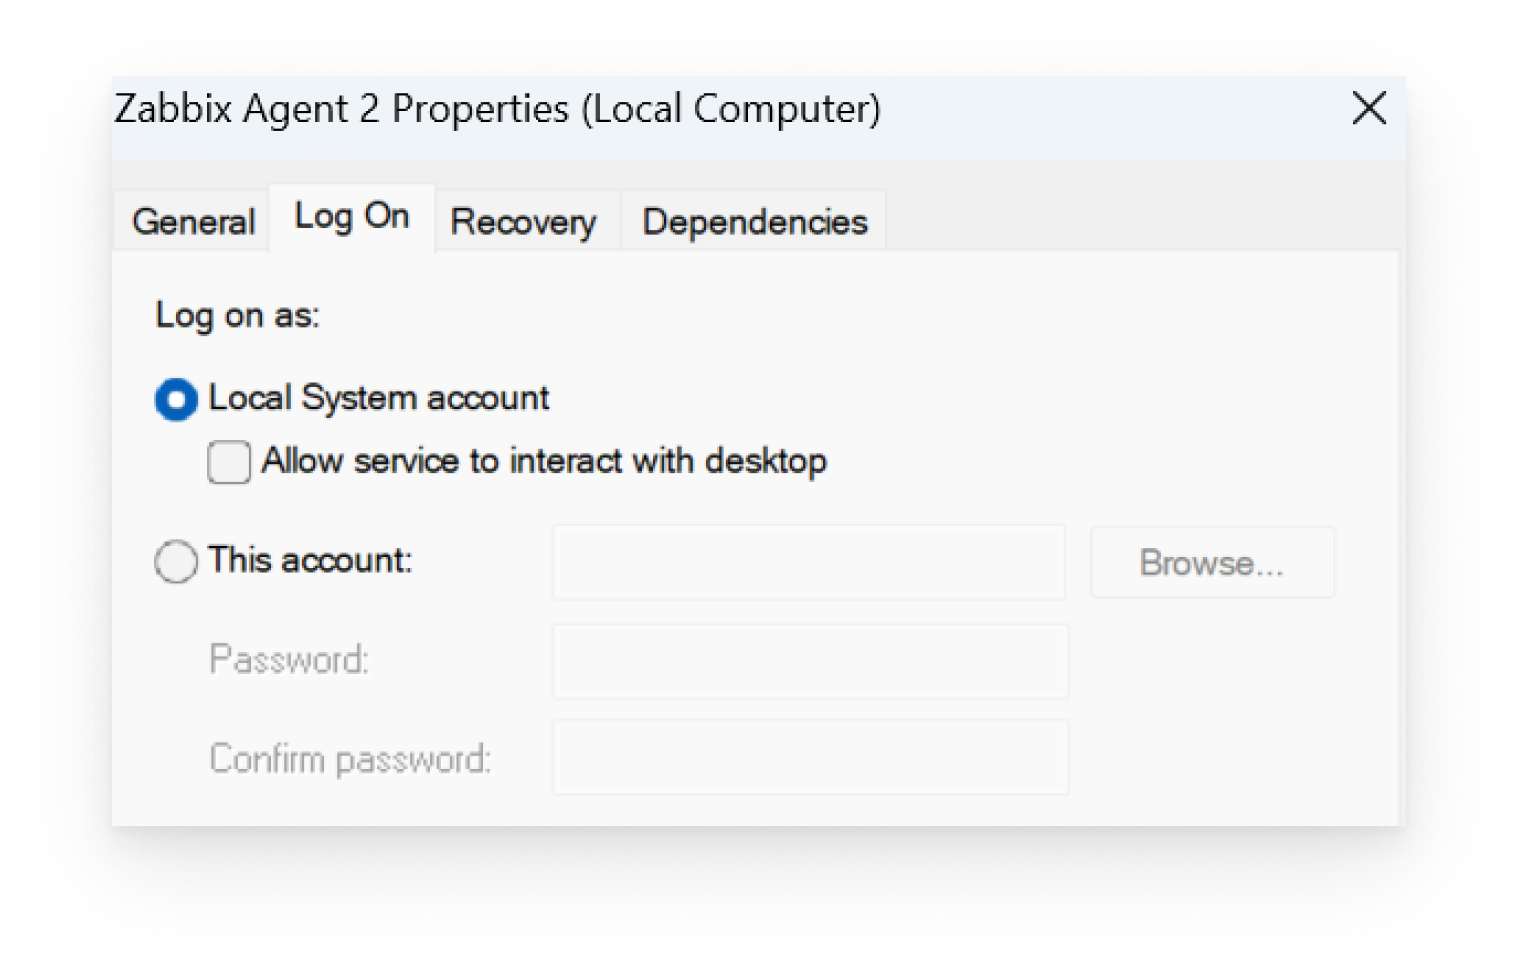
As a result of both approaches, Zabbix agent will be installed and run as a Windows service. By default the agent runs under the Local System account (Having unrestricted access to local system resources) – this can and should be adjusted based on your organizational security policies.
Additional Zabbix agent 2 plugins
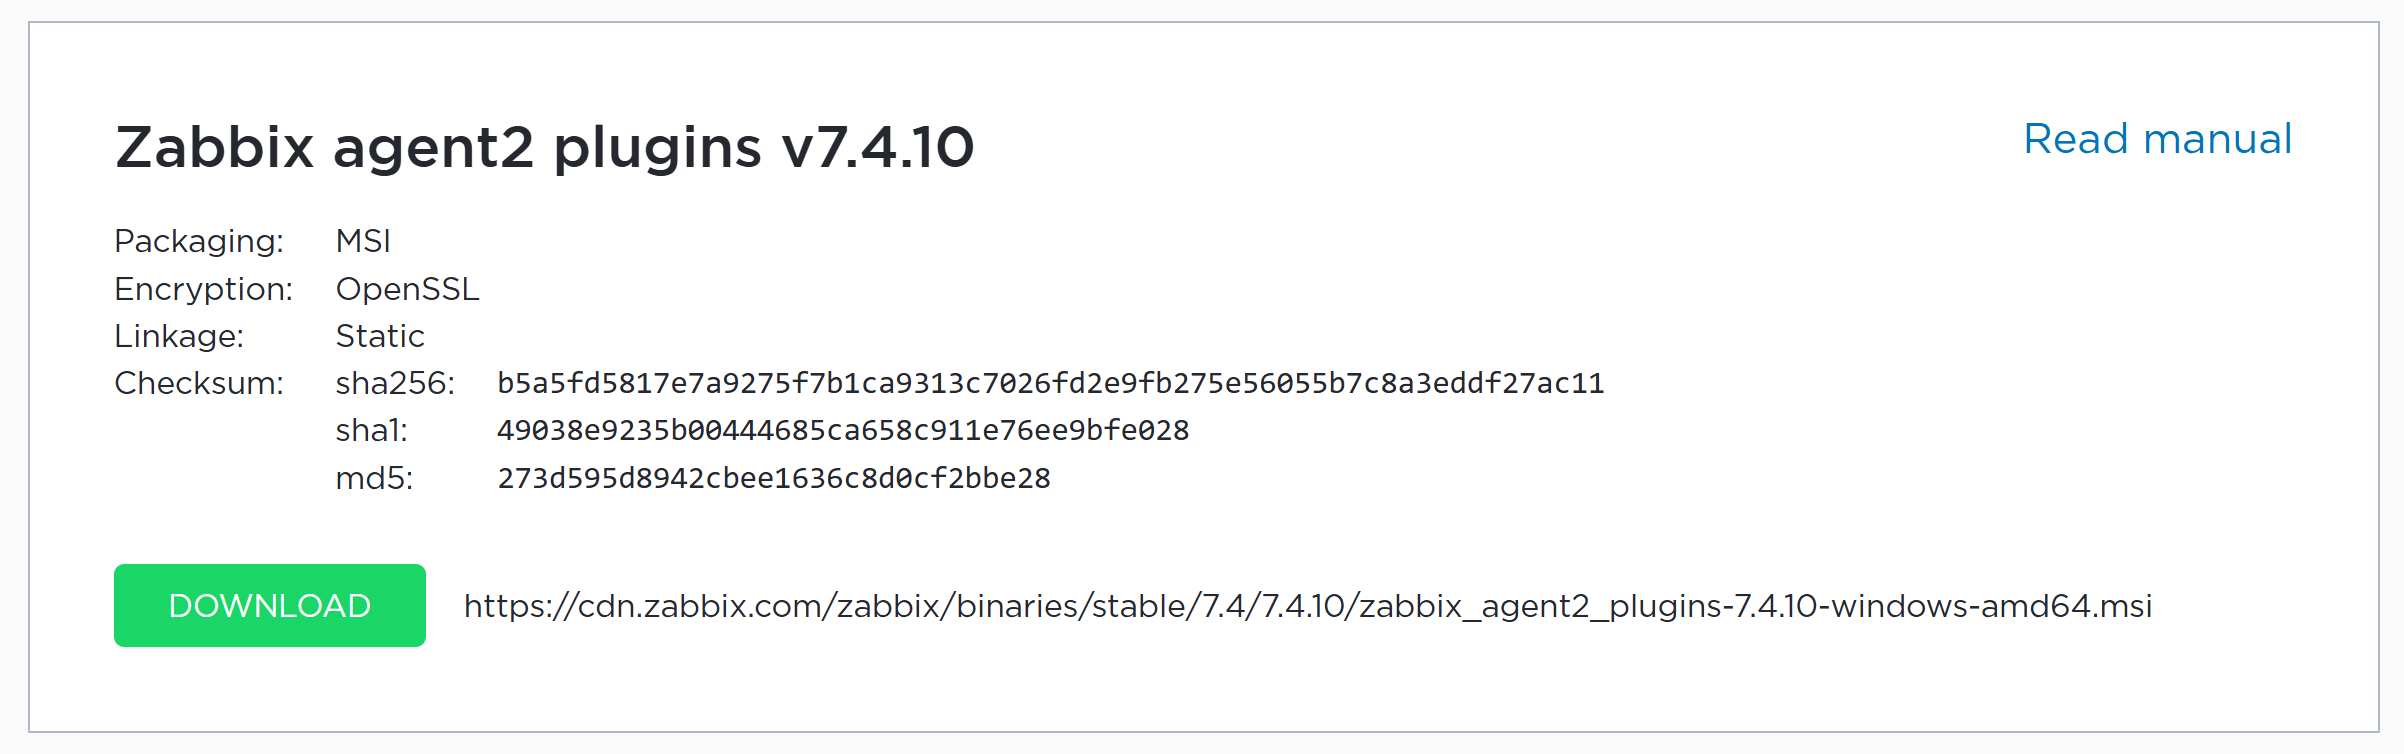
Multiple Zabbix agent 2 plugins are provided in a separate package, which can also be installed via the MSI installer. The following plugins have to be installed via the dedicated Zabbix agent 2 plugins package:
- Ember plus
- MongoDB
- MSSQL
- NVIDIA GPU
- PostgreSQL
Configuring a Windows host in Zabbix
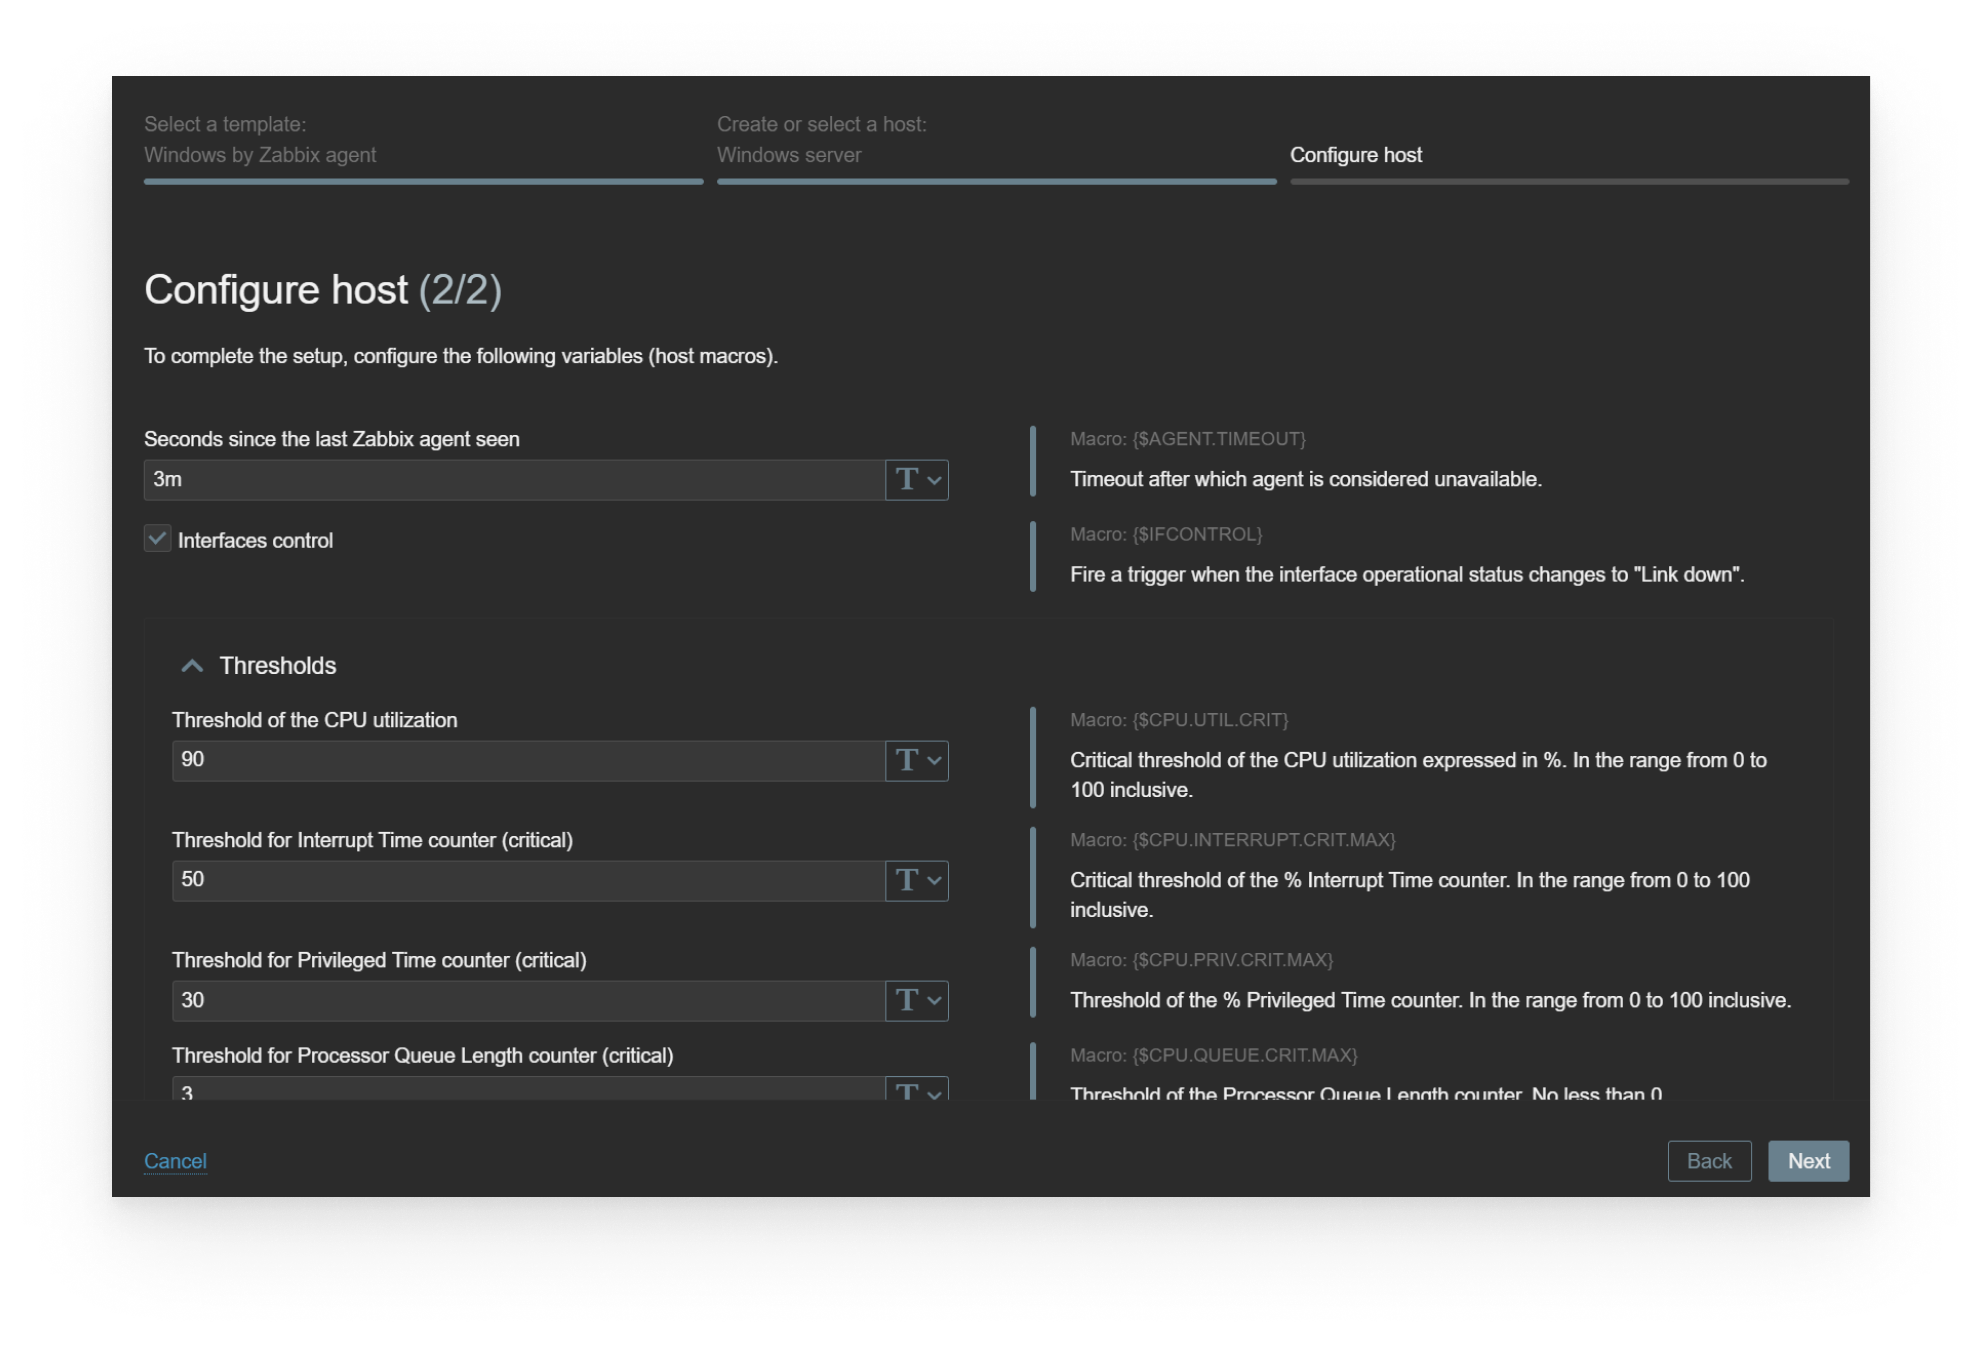
The quickest way to get started once the agent is deployed and configured, is to create a Windows host in Zabbix and use one of the official Zabbix templates on this host. The host can be either created manually or by using the Host Wizard for a more guided experience (Host Wizard is available starting from Zabbix 7.4).
After you have assigned the template, adjust the macros used for trigger thresholds and low-level discovery filters on the host level, so they fit your individual requirements. (Once again – the Host Wizard will guide you through this process during the host creation. Otherwise – open the Macros section in the host configuration and adjust them manually)
Official Zabbix templates for Windows environments
Zabbix provides a variety of templates for Windows OS and application monitoring:
- Windows by Zabbix agent
- MSSQL by Zabbix agent 2
- Microsoft SharePoint by HTTP
- Microsoft Exchange Server 2016 by Zabbix agent
- IIS by Zabbix agent
The templates contain static items, triggers, graphs and dashboards as well as a variety of low-level discovery rules to discover resources such as:
- Network interfaces
- Physical disks
- Windows services
- MSSQL Databases
- IIS Application pools
- SharePoint directories
- Exchange services
- And much more!
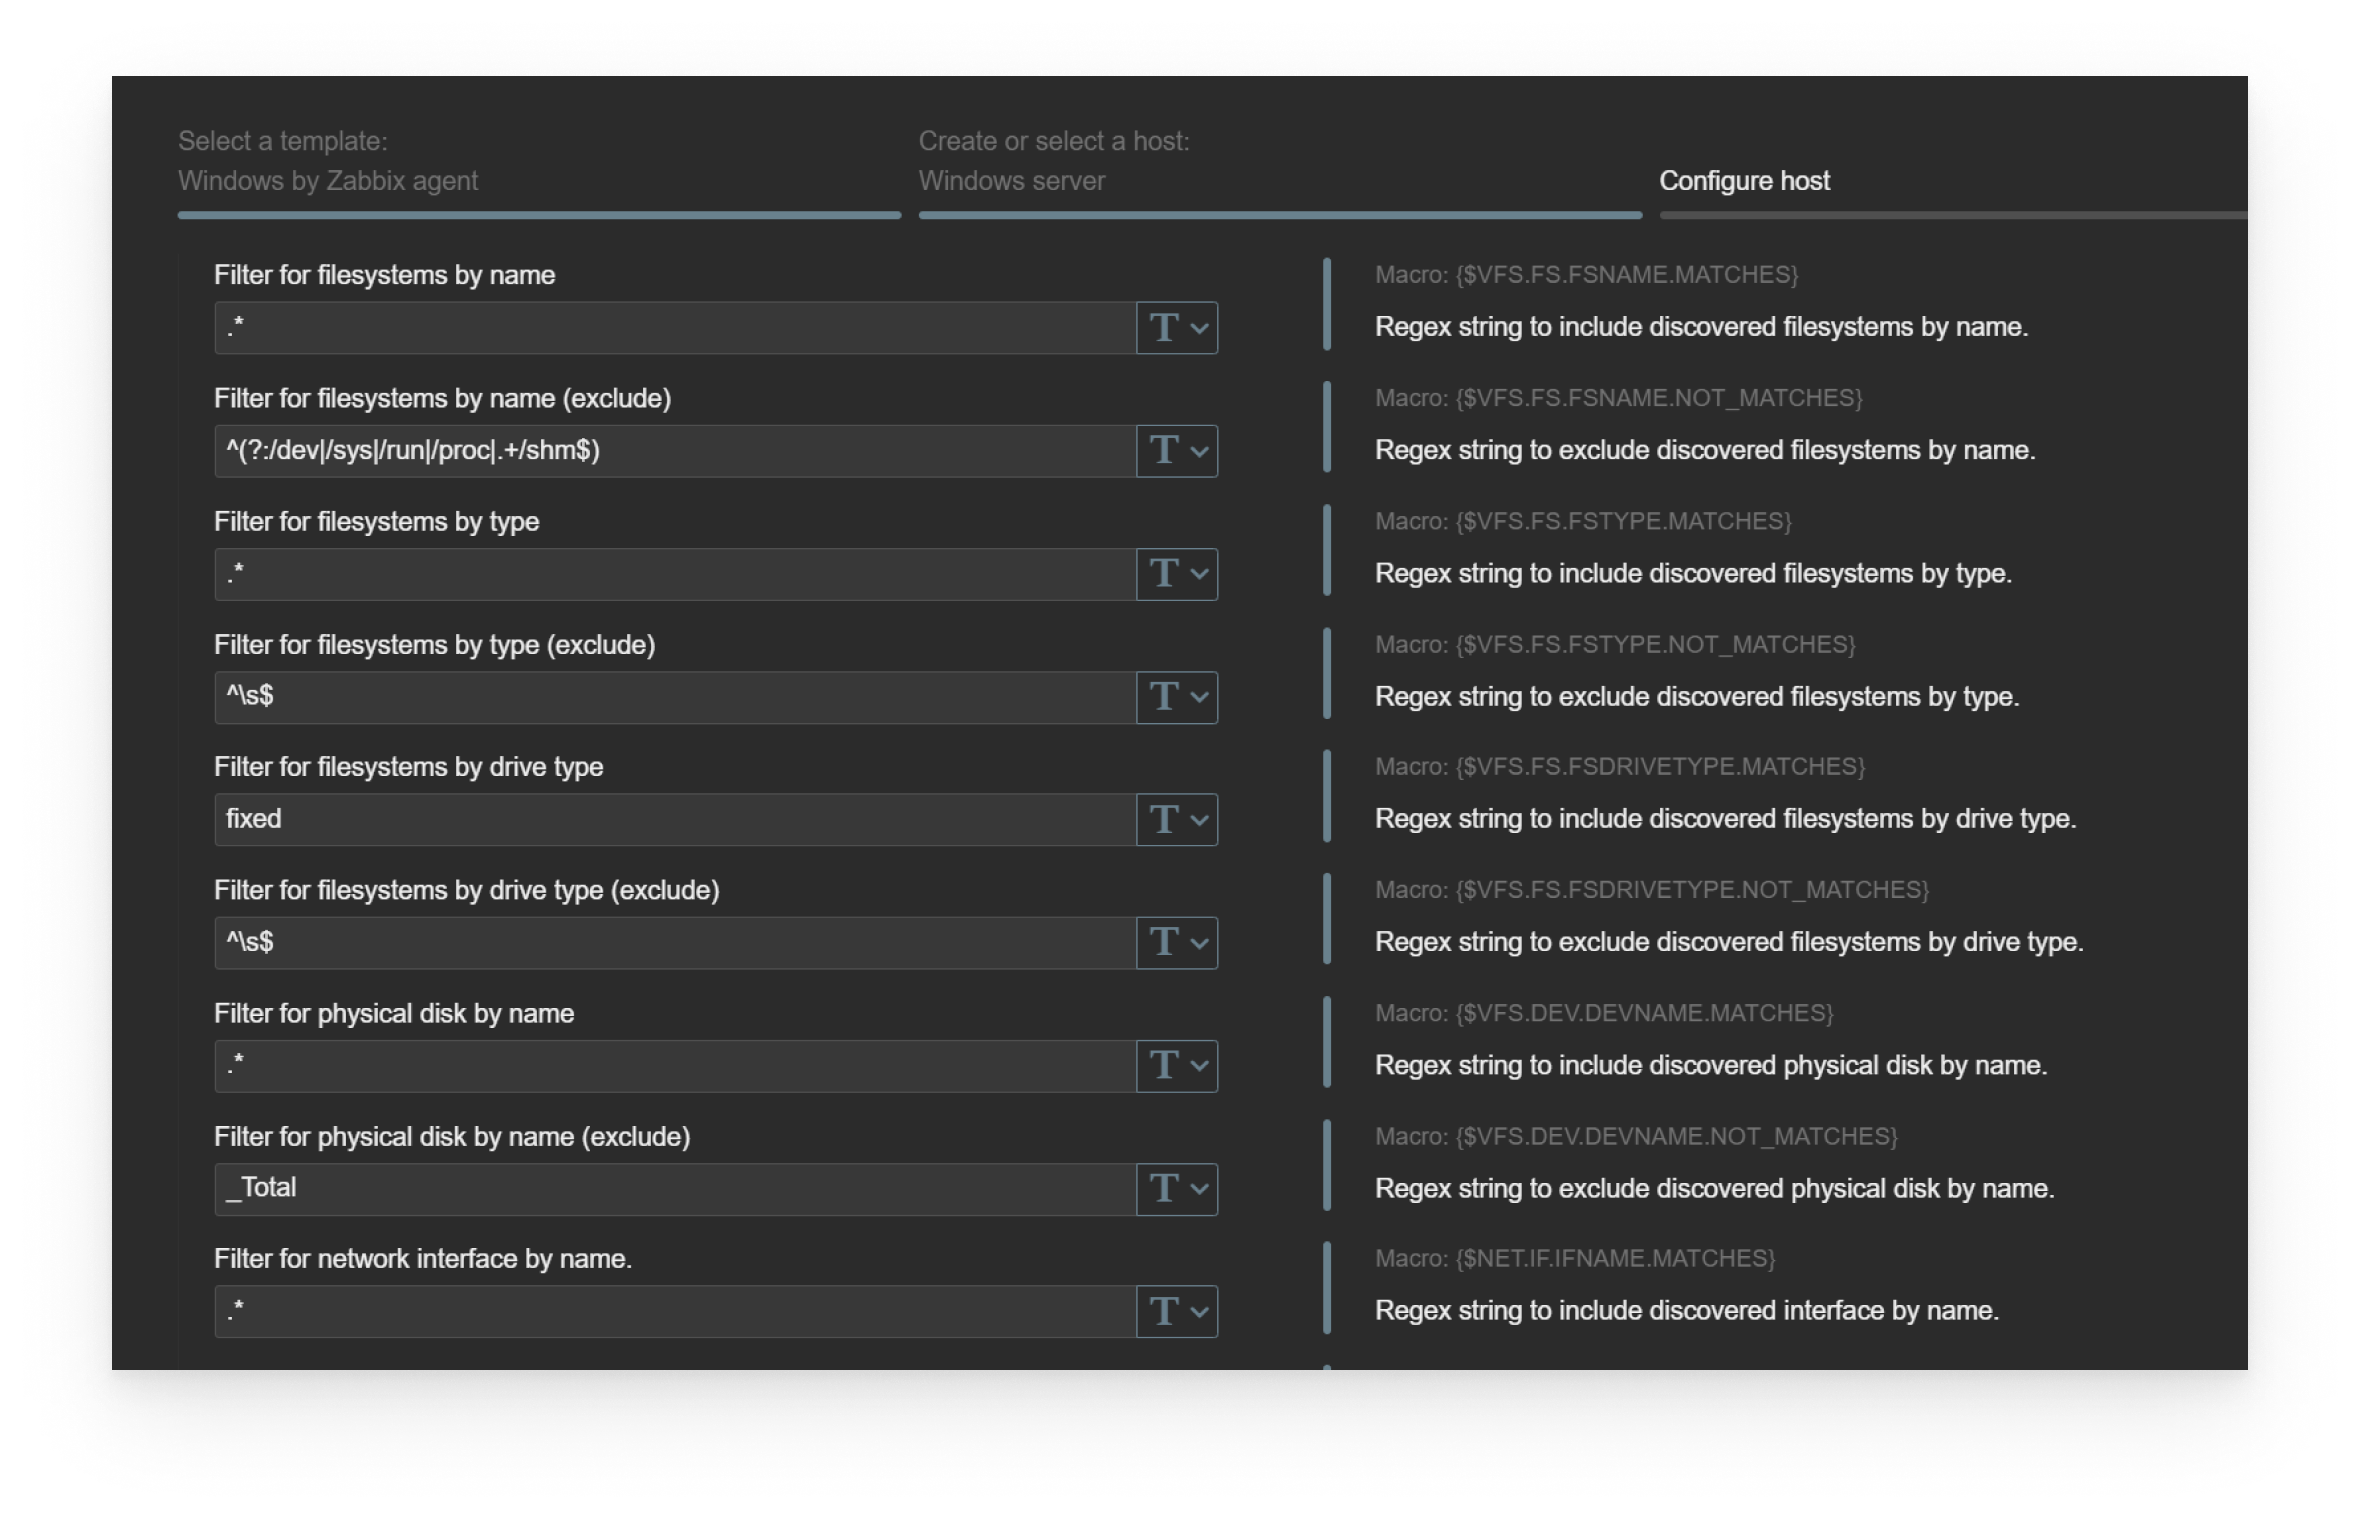
Depending on the application, additional configuration might be required on the application side. The required configuration steps are documented in the corresponding integration pages on our website.
Performance counters and WMI queries
Performance counters are used both in our official templates and are also a common way how existing templates can be extended and templates for other Windows applications can be built.
Performance counter monitoring is done by using a Zabbix agent item key – perf_counter[]
With this approach you can configure your Zabbix agent to collect any supported performance counter value. For example, here’s a performance counter item key for monitoring IIS application pool state:
perf_counter[“\APP_POOL_WAS(Customer Portal)\Current Application Pool State”]
The item key can also use performance counter indexes (numeric performance counter representations).
To ensure that performance counter items remain portable across different Windows hosts with different Windows locales, Zabbix provides English performance counter item key – perf_counter_en[].
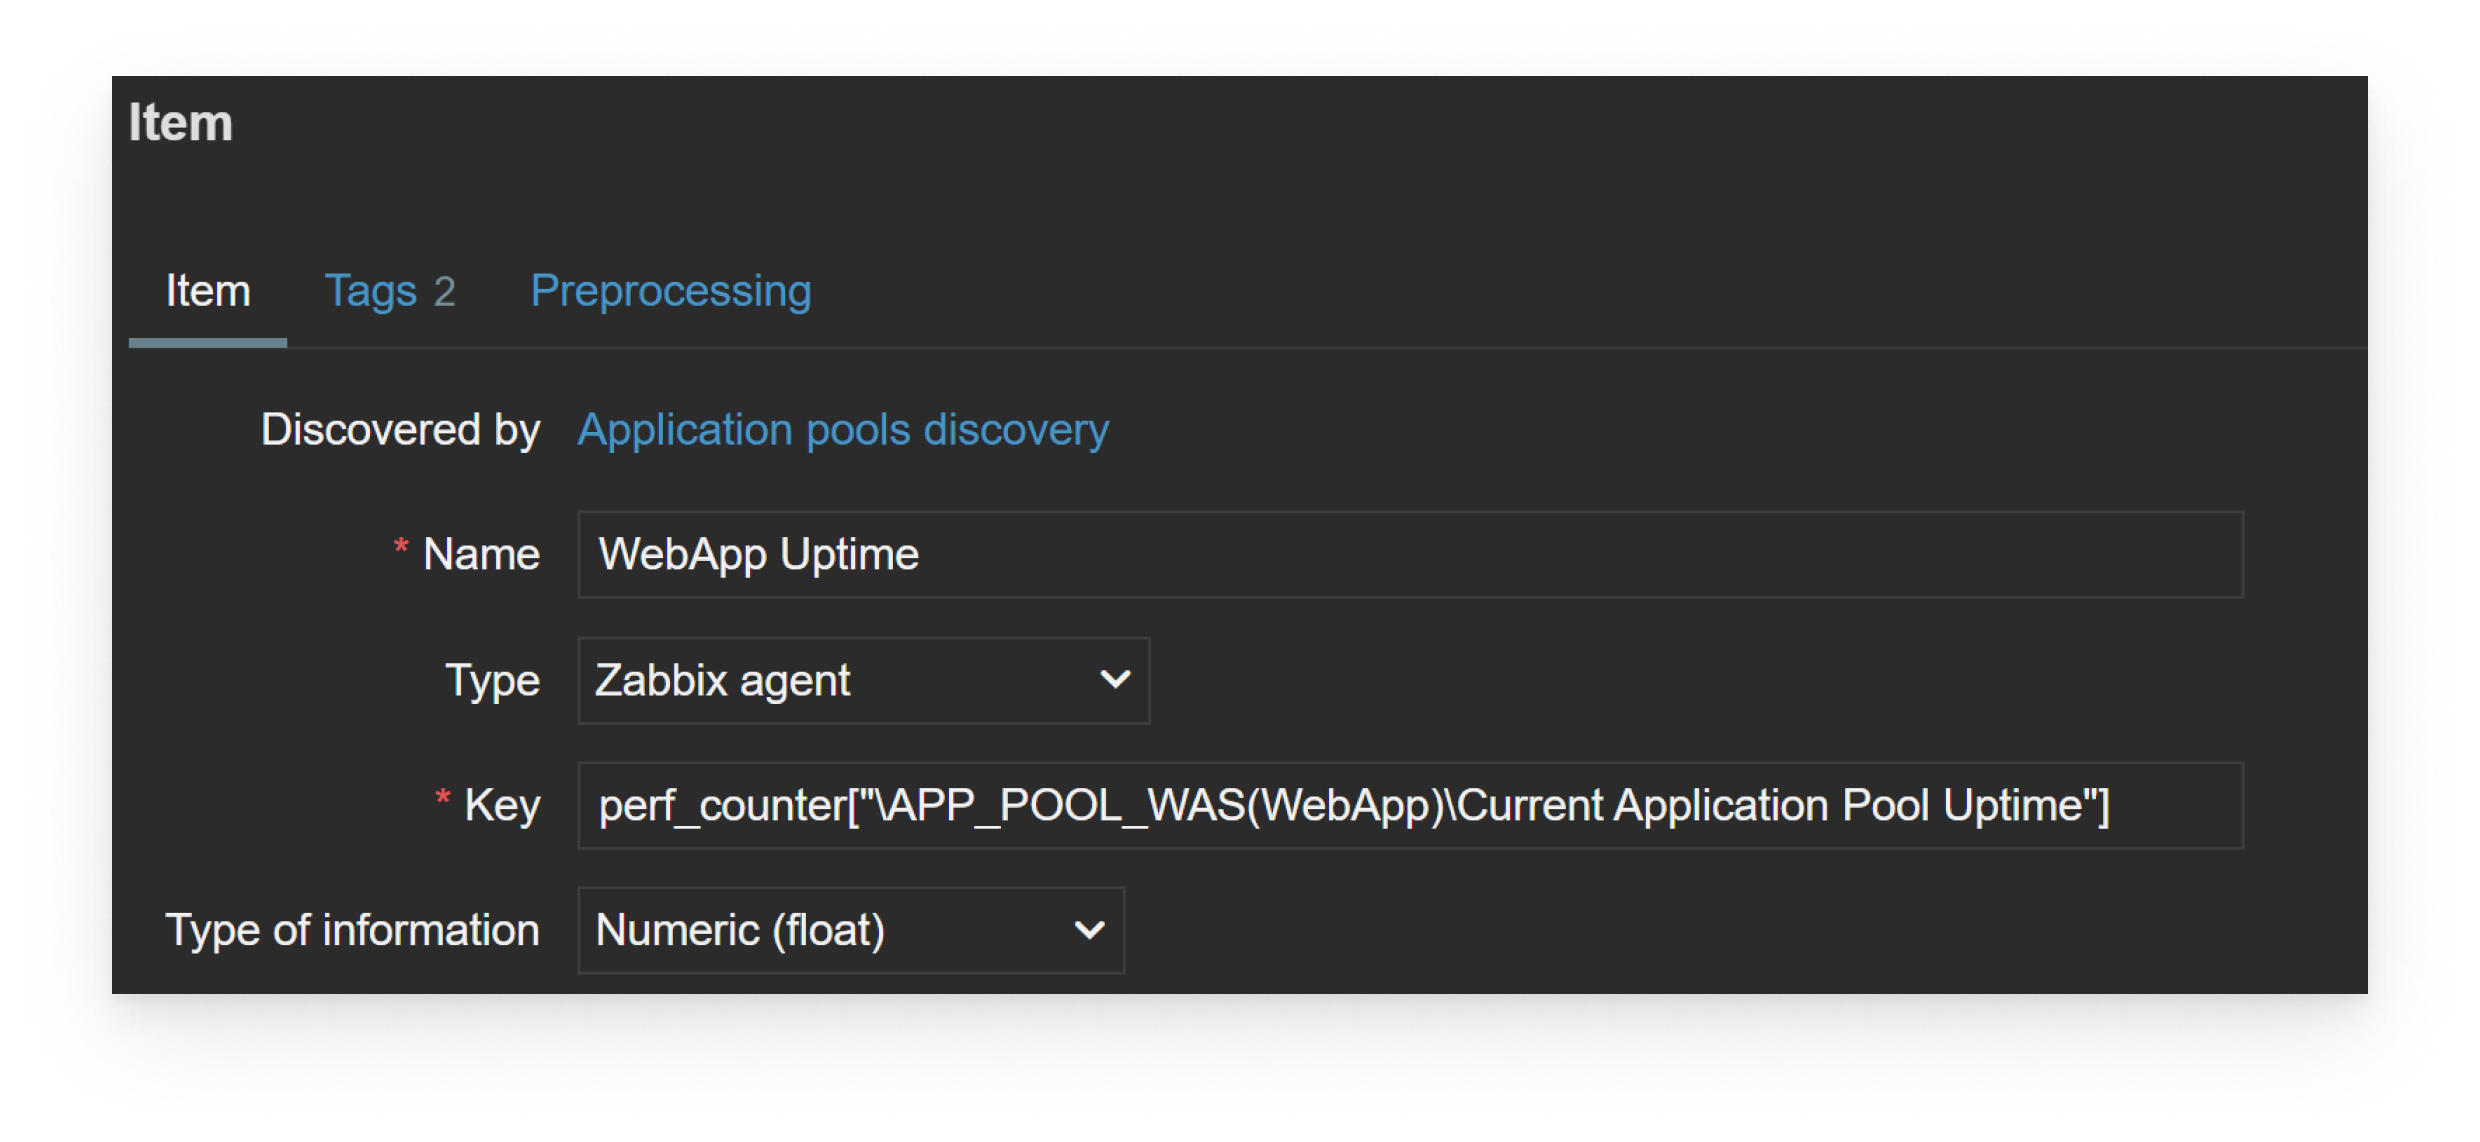
In addition to performance counters, Zabbix agent can also execute WMI (Windows Management Instrumentation) queries.
Two keys can be used to collect WMI data:
- get[<namespace>,<query>] – return the first selected object
- getall[<namespace>,<query>] – return the whole response in JSON (Can be used for low-level discovery)
For example – return the status of the first physical disk: wmi.get[root\cimv2,select status from Win32_DiskDrive where Name like ‘%PHYSICALDRIVE0%’]
Windows log monitoring
Zabbix agent provides 2 item keys specifically for Windows event log monitoring:
- Collect the event log entry matching the item key parameters: eventlog[name,<regexp>,<severity>,<source>,<eventid>,<maxlines>,<mode>]
- Collect the number of matching event log entries ofr a time period: count[name,<regexp>,<severity>,<source>,<eventid>,<maxproclines>,<mode>]
The event log entries can be filtered by log name, log contents (via a regular expression), log severity, source, and event ID.
For example, we might want to react only to log entries in the System log with entry severity matching Warning or Error.
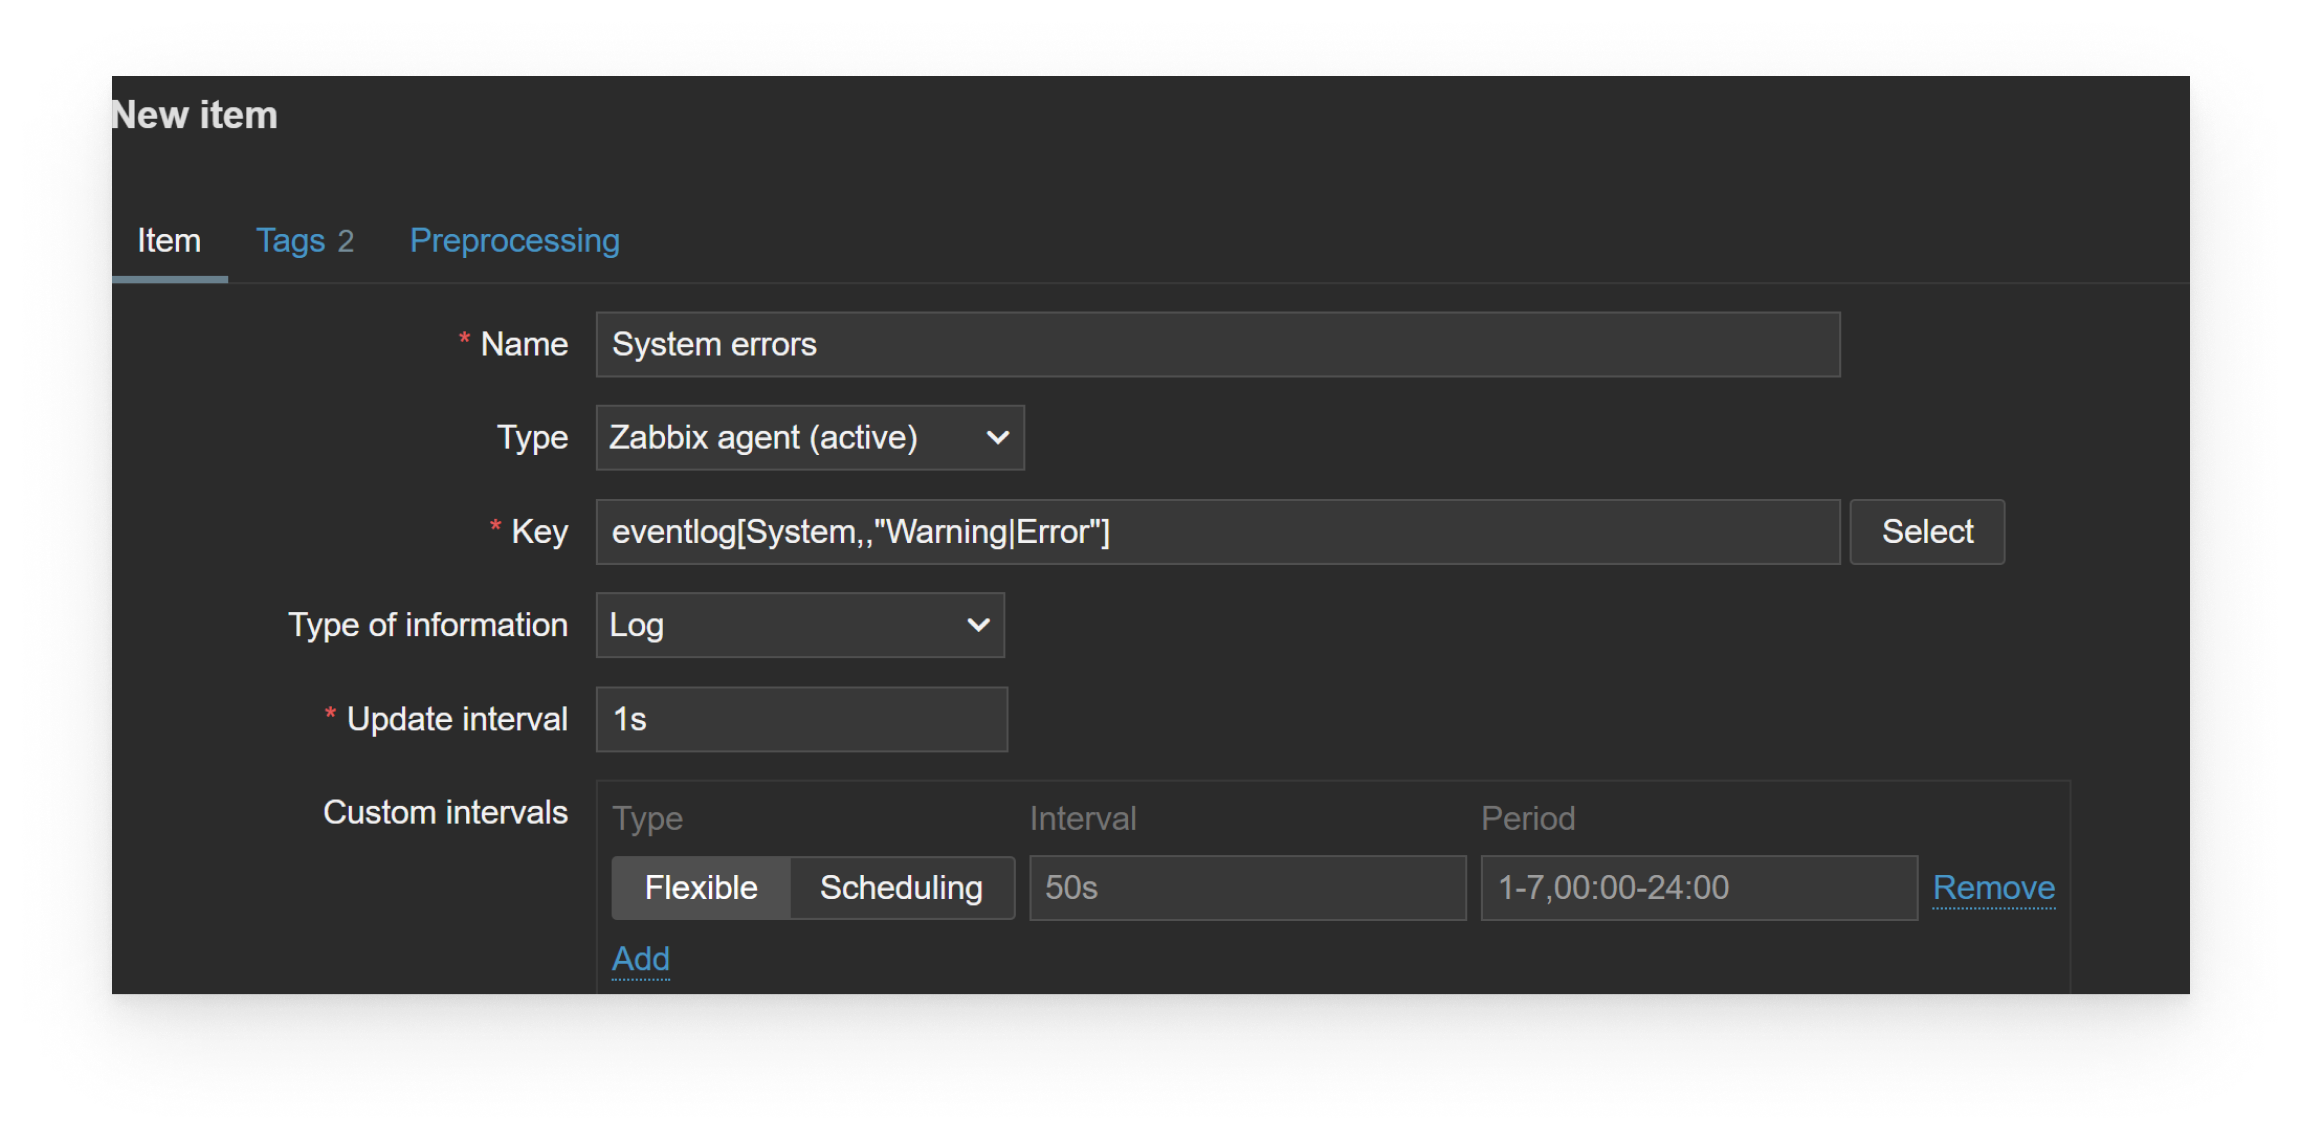
Here the regular log monitoring guidelines apply – it’s supported only by Zabbix agent active checks with the recommended update interval of 1 second (except for eventlog.count) and have a dedicated Type of information with a unique set of configuration settings.
Extending Zabbix agent on Windows
In addition to custom performance counters and WMI queries, Zabbix agent installations on Windows installations can be extended in standard Zabbix ways:
- Defining Zabbix agent User parameters with custom item keys
- Using Zabbix agent system.run item to run custom scripts and commands
Since Zabbix agent is language-agnostic, we can utilize Windows-specific PowerShell scripts or commands to collect custom data:
For example, we can use PowerShell to get a list of pending Windows updates:
UserParameter=GetUpdates,powershell Get-WindowsUpdate
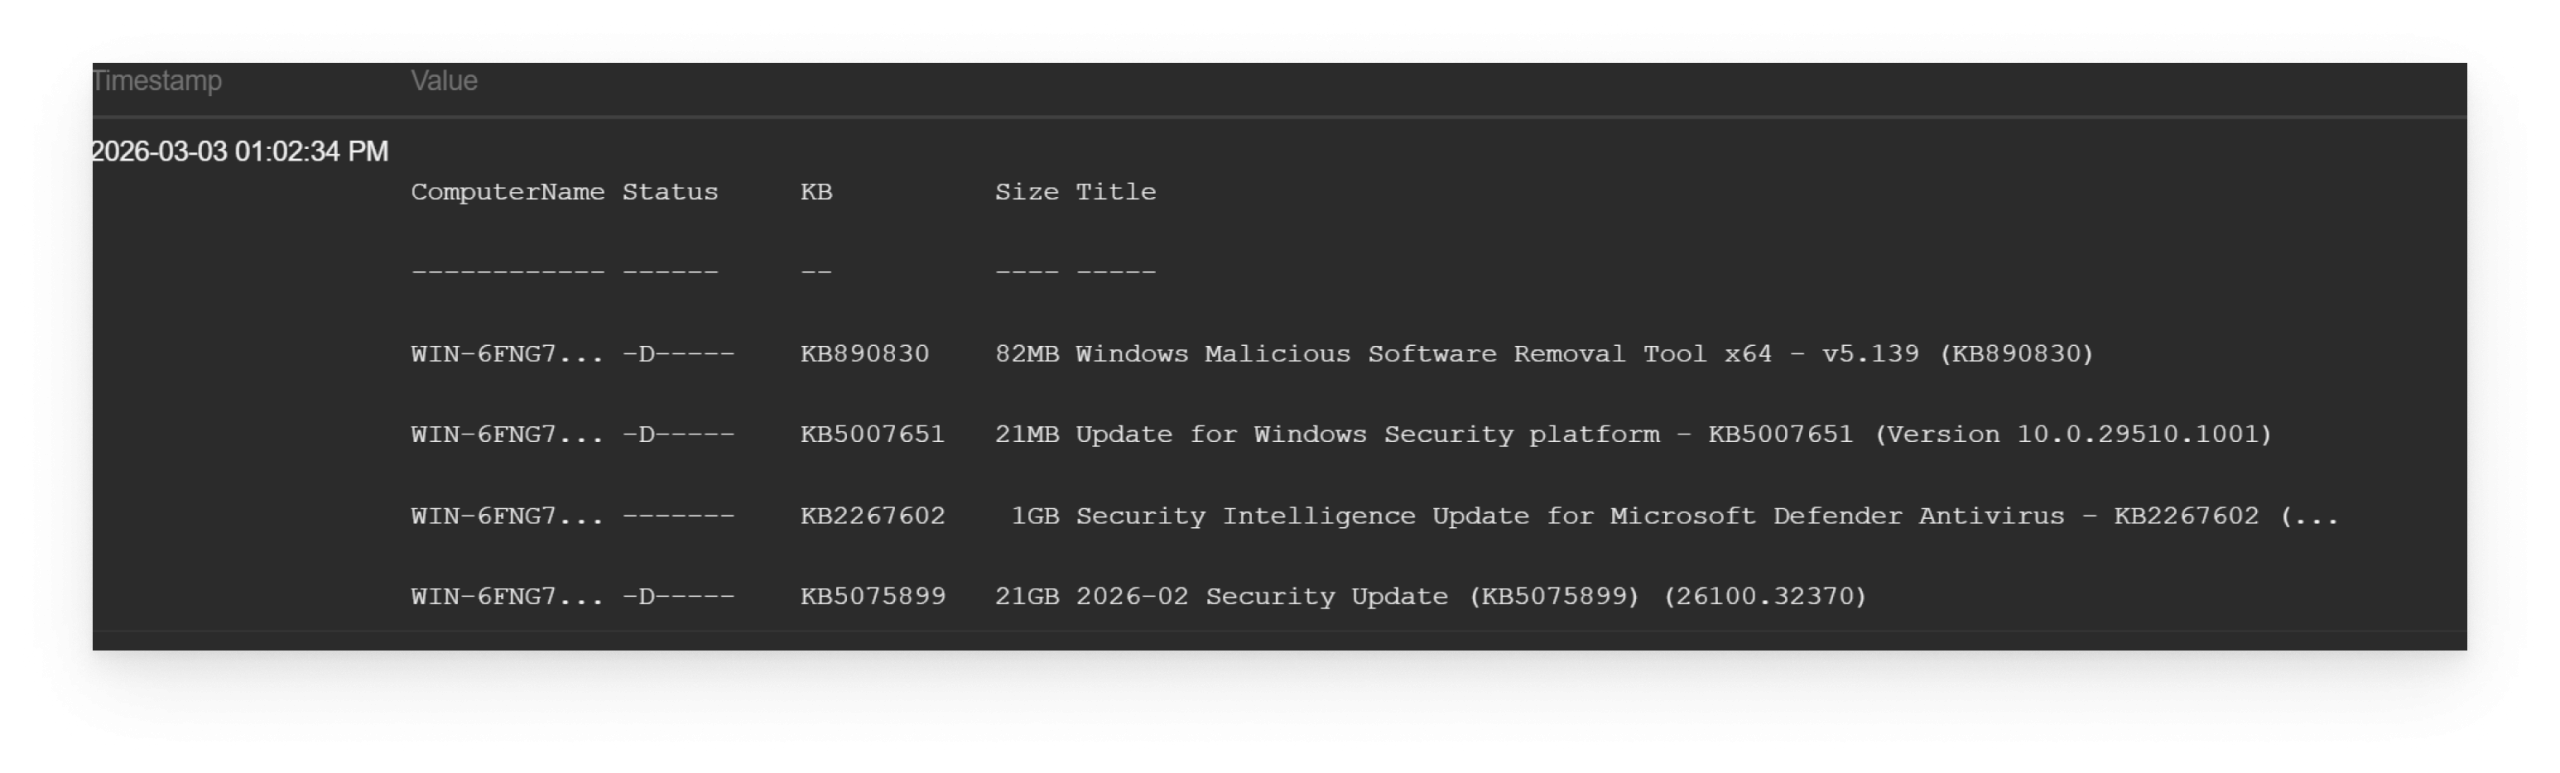
Native Zabbix features such as preprocessing and dependent items can be applied to the collected data to transform or extract the required values or utilize low-level discovery features to automatically create items and triggers based on the ouput of the script.
Finally, the collected data can be used to create different views of your Windows server resource usage, application states and any other collected metrics.
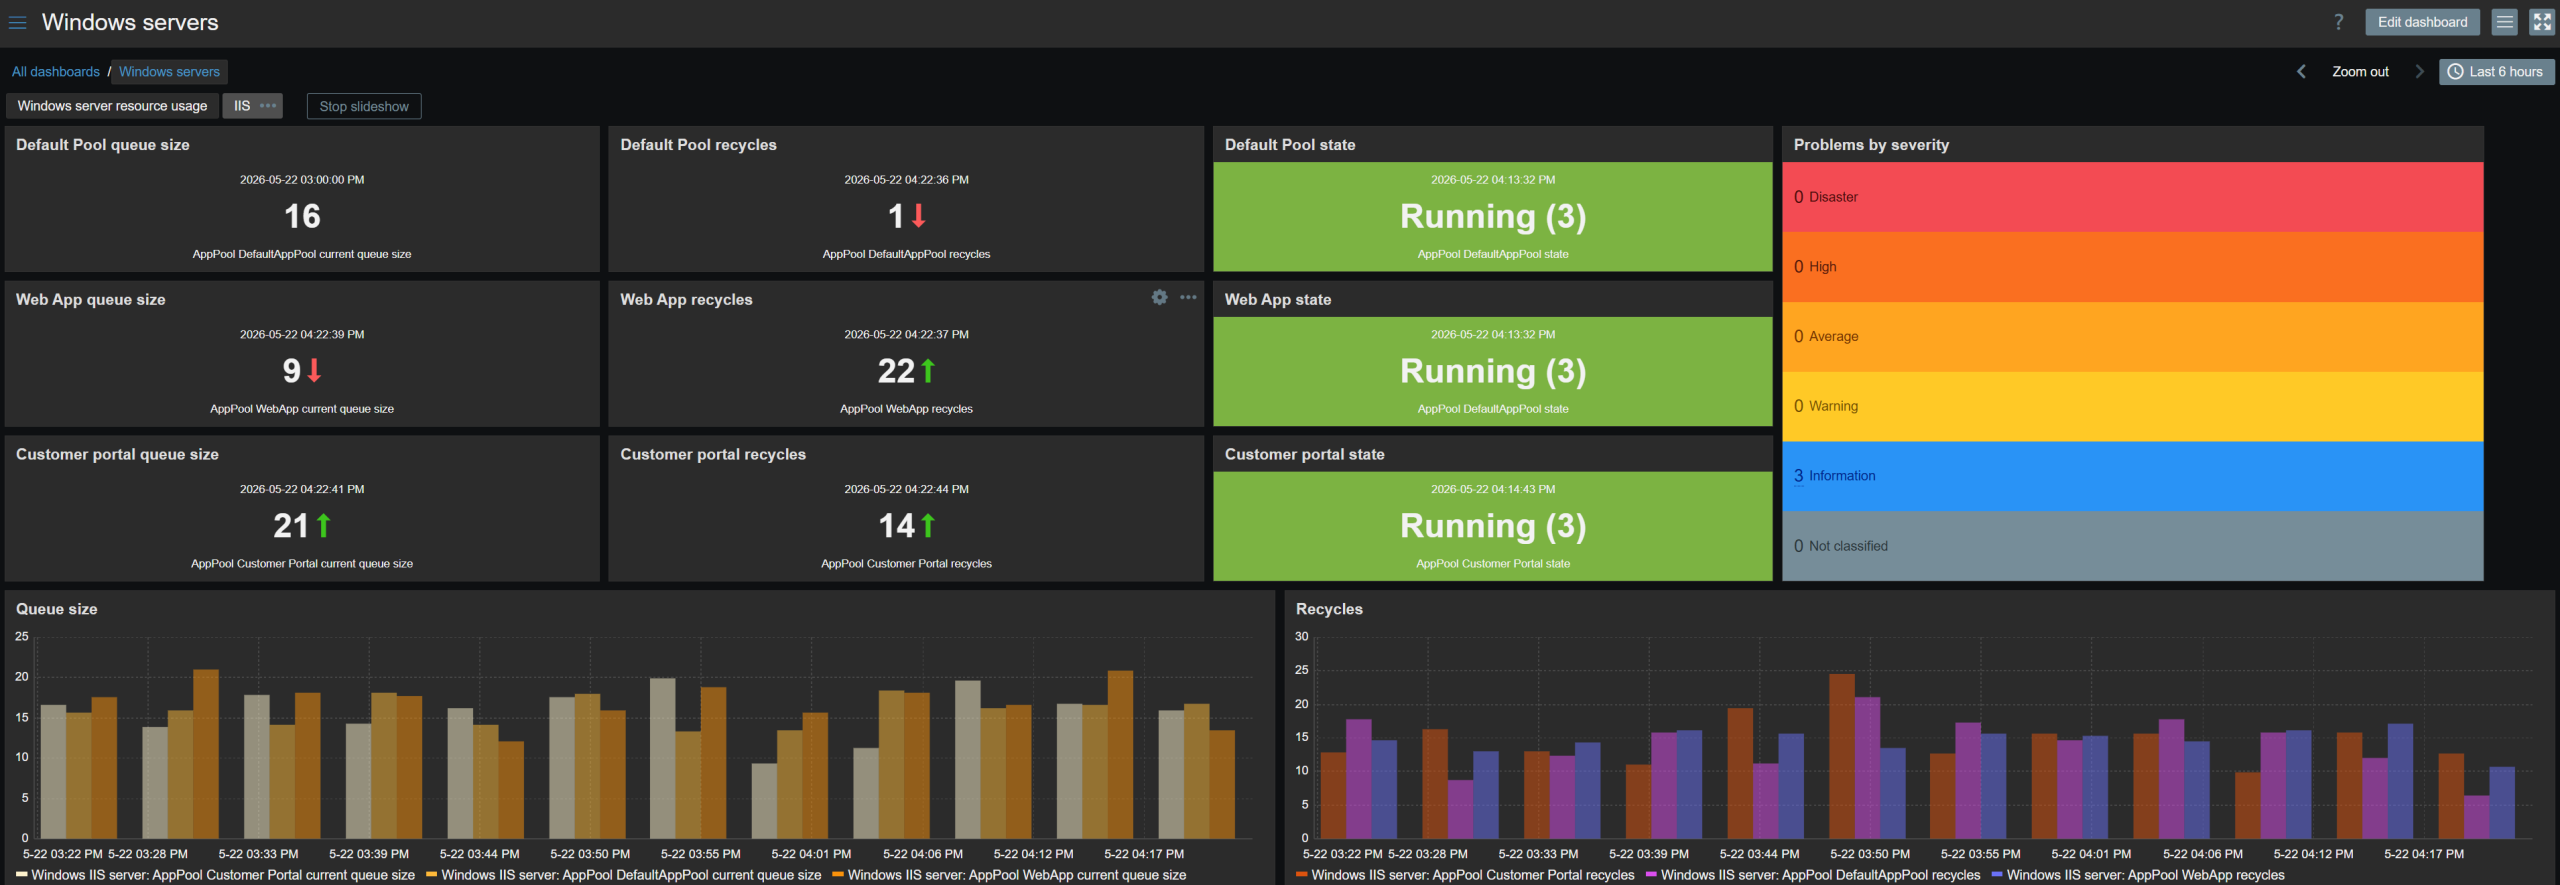
The post Windows Monitoring with Zabbix appeared first on Zabbix Blog.
Prompt Injections for Defense
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2026/08/prompt-injections-for-defense.html
This seems to work:
Researchers from Tracebit on Monday said they found that placing prompt injections alongside passwords, cryptographic keys, and other secrets stored on Amazon Web Services was often all that was needed to shut down attacks from AI hacking agents. The prompts direct the attacking LLM to perform an action forbidden by its guardrails, the safety barriers AI developers erect to prevent it from taking harmful actions. The LLM responds by shutting down.
Examples are a prompt that orders the LLM to provide steps for developing inhalable Anthrax spores, or, in the case of LLMs from Chinese developers, make references to the iconic Tank Man from the 1989 Tiananmen Square massacre. Once the LLM encounters these forbidden commands, it no longer follows its existing commands. The researchers have named the technique context bombing.
Of course, this only works against agents that have guardrails. As we start to see more locally run AI models, we’ll see more attackers using LLMs with no guardrails.
Tamron 12–20mm vs Nikon Ultra Wides — Which One Wins?
Post Syndicated from Matt Granger original https://www.youtube.com/watch?v=zwvldQ1Z13k
Geology Building
Post Syndicated from xkcd.com original https://xkcd.com/3284/
Grab Bench: Evaluating AI on Grab-shaped production work
Post Syndicated from Grab Tech original https://engineering.grab.com/grab-bench-evaluating-ai
Introduction
What worried us wasn’t the hallucination, it was the subtle plausibility. Answers an engineer could easily read past and accept: a right-looking Structured Query Language (SQL) query, a plausible tool call, an innocent profile update, or a patch that satisfied the surface tests.
When we analyzed the row-level failures, a clear pattern emerged:
- SQL generation: kept the query shape but changed the underlying metric.
- Tool calling: selected the right tool family but drifted on parameters.
- Profile updates: cited every event instead of only the evidence that supported the claim.
- Coding agents: passed visible tests while missing a hidden stateful invariant.
Grab Bench bridges this exact gap. Grab Bench is a configurable eval (evaluation) harness for artificial intelligence (AI) systems on Grab-shaped work. It runs model providers through task plugins, records one row per case/model pair, and uses deterministic scorers or large language model (LLM) judges depending on the task. We treat the eval like software: version it, run baselines, keep score records, and make the failure modes visible enough for a team to debug.
This write-up focuses on the design choices behind that work.
The problem: plausible is not correct
Public leaderboards are still useful; we read them too. They just answer a different question. A product team needs to know whether a model can preserve a metric definition, obey an internal tool contract, stay cautious with weak evidence, or make a code change without breaking behaviour hidden from the prompt.
The hard part is that real examples are rarely reusable as-is. Production traces, schemas, user records, and internal workflows need protection. So the benchmark has to preserve the shape of the work without depending on the work itself.
That constraint shaped Grab Bench from the beginning. Some surfaces stay internal. Others use synthetic or redacted cases. Either way, the case has to keep the thing that makes the work hard: metric faithfulness, tool-parameter discipline, evidence grounding, safety boundaries, or repository-level behaviour.
What Grab Bench runs
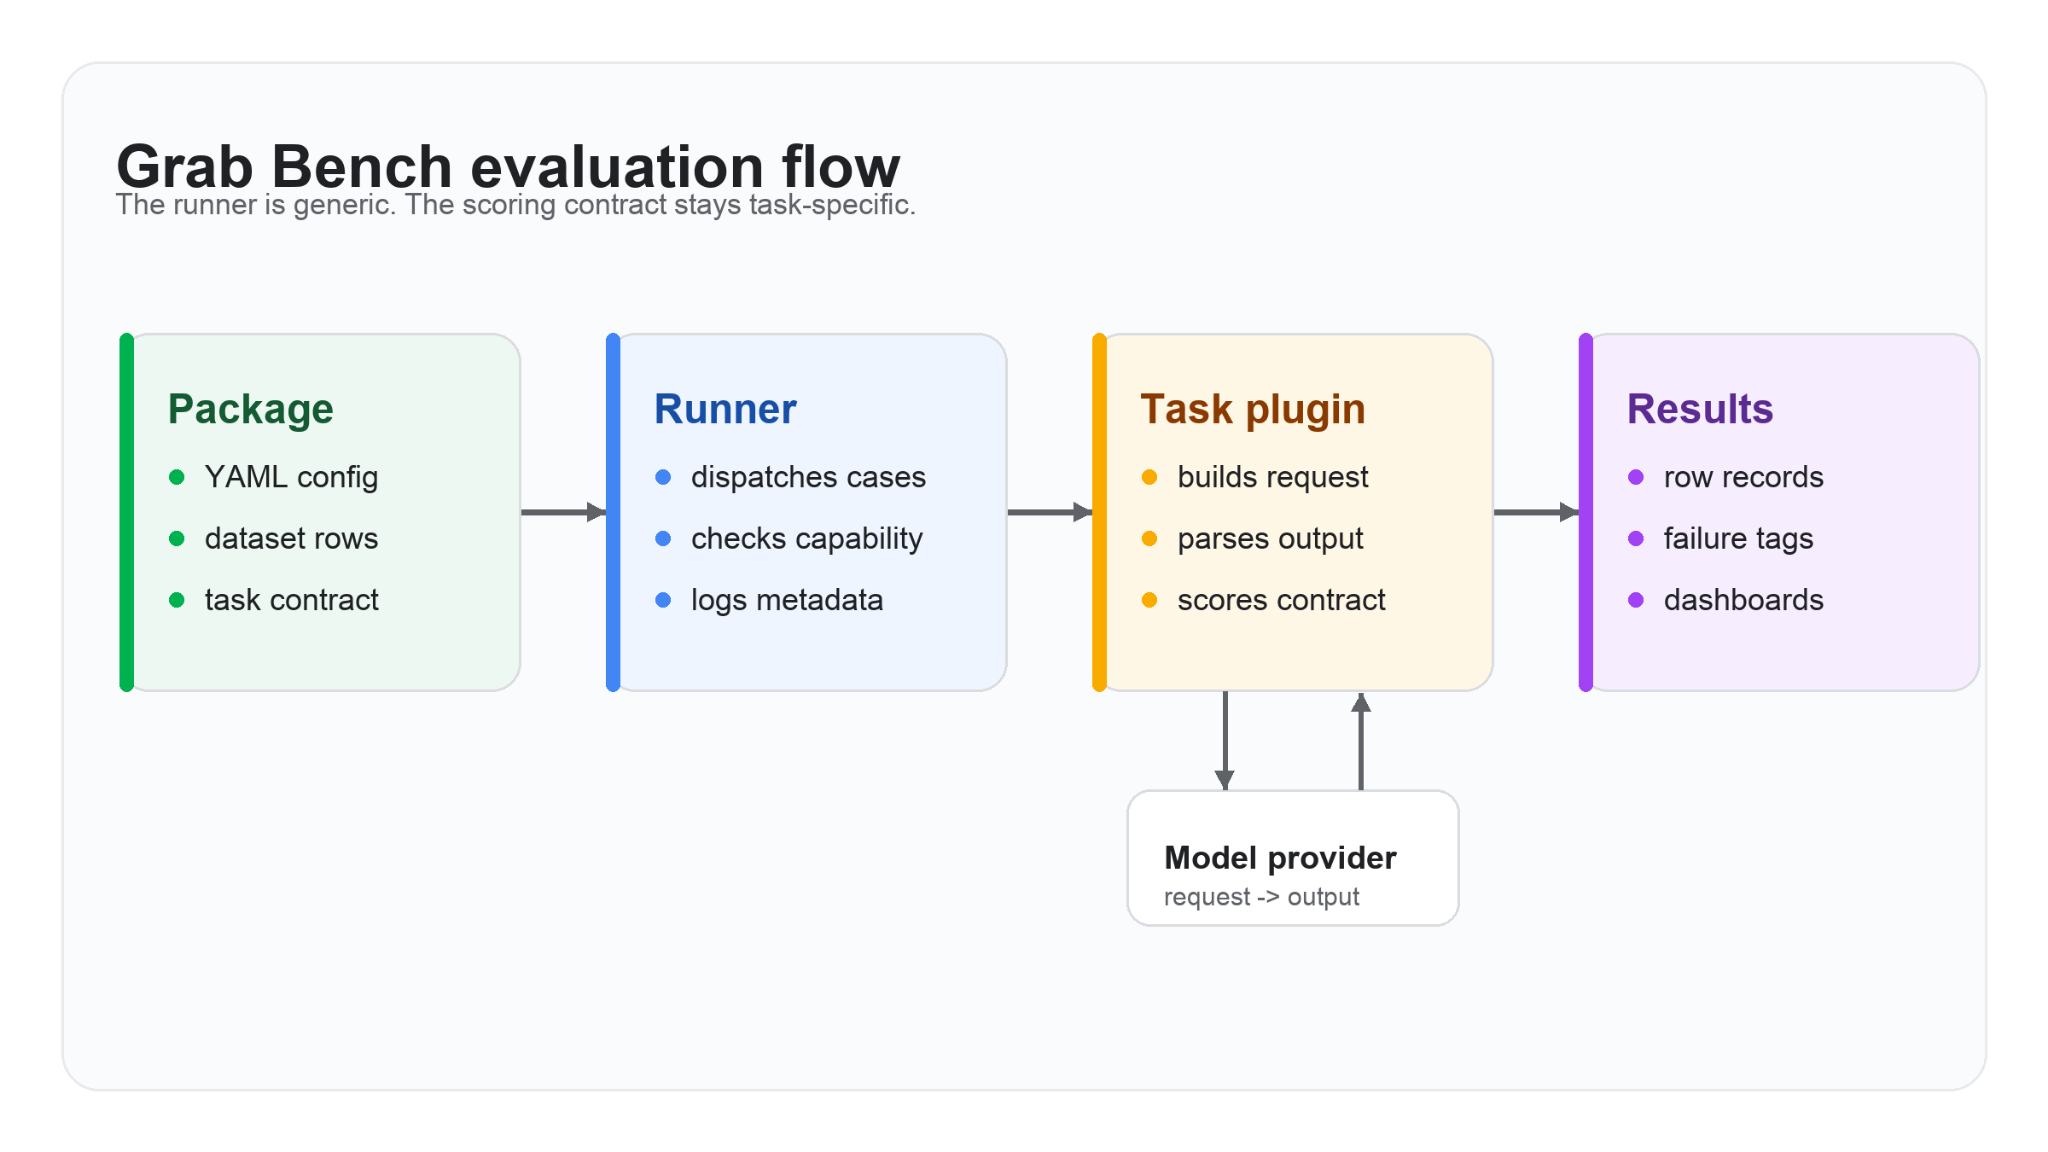
The harness is deliberately ordinary. A YAML configuration defines providers, models, task settings, sampling, concurrency, judge settings, and output paths. The runner loads rows, checks whether each model supports the required modality and application programming interface (API) family, calls the task plugin, and writes row-level records plus model summaries for dashboards.
The unusual part is that each task owns its contract:
- Query generation cares about preserving metric and schema intent.
- Tool use compares canonical tool names and parameters.
- Multimodal pair matching scores constrained yes/no decisions.
- Passenger-profile reasoning checks grounded claims, evidence, uncertainty, action quality, and safety.
- Agentic coding runs visible and hidden workspace tests, plus hard-failure and anti-gaming checks.
This is why the row record matters. A leaderboard can tell us that one model is ahead. It cannot tell us whether the loss came from a fabricated evidence identifier (ID), a weak action, a hidden invariant, latency, cost, or a genuine capability gap.
Each run also keeps the unglamorous fields that make reruns possible: token use, latency, judge latency where applicable, skip reasons, resolved configurations, and dashboard-ready summaries. Without those fields, the next comparison starts from memory instead of evidence.
Figure 1 is deliberately boring: add a plugin; providers, records, and dashboards stay shared.
Design choice 1: make the cases safe, not generic
A useful eval case should feel familiar to the people who own the system. It should include distractors, stale context, ambiguous evidence, and the kind of boundary conditions that make production work tricky.
In passenger-profile reasoning, each case is a synthetic evidence ledger: rides, food, support, app events, saved places, promotions, and noise. All cases use synthetic data with no live user records. The model must return strict JavaScript Object Notation (JSON). Claims must come from an ontology; values must be valid for that claim; evidence IDs must exist; weak or sensitive inferences should be suppressed, not laundered into confident prose.
The scorer is deliberately mechanical where it can be: schema validity, claim correctness, evidence faithfulness, confidence calibration, action quality, and safety. It distinguishes required claims from acceptable auxiliary claims and forbidden claims, so a model can get credit for useful extra evidence without getting a pass on unsafe or unsupported inferences.
A simplified case might ask whether a passenger has a stable weekday commute:
-
The evidence ledger contains repeated morning rides from a home-like saved place to an office-like area, plus unrelated food orders and stale support contacts.
-
A good answer returns a claim such as
weekday_commute = likely_home_to_office_commute, cites only the commute evidence IDs, and keeps confidence within the allowed range. -
The scorer checks that the claim and value exist in the ontology, that every cited evidence ID exists, and that the cited rows actually support the claim.
-
If the model cites every event, fabricates an ID, adds a dietary-preference claim from one old order, or recommends an unsafe action, the row gets explicit failure tags or a score cap.
-
The result is still a number, but the row also says what failed, which is what an engineer needs to fix the prompt, scorer, data, or model choice.
For agentic coding, the repository is synthetic too, but it asks for a real-shaped change: default ride insurance across backend services, API compatibility, mobile helpers, analytics events, rollout controls, migration compatibility, idempotency, concurrency, and cancellation lifecycle. A patch that only satisfies visible tests is not enough.
The safety comes from using synthetic data. The pressure comes from keeping the real contract intact.
Design choice 2: score contracts, not confidence
LLM judges are useful for open-ended tasks such as SQL, where correctness can depend on business intent and query shape. But for many surfaces, the benchmark should not ask another model whether an answer seems good.
Grab Bench uses deterministic scoring when the task contract allows it. Passenger-profile reasoning scores ontology values and evidence IDs. Tool use compares canonical tool names and parameters. Multimodal pair matching scores exact labels. Agentic coding scores visible and hidden tests, maintainability, efficiency, and hard-failure gates.
The audit trail is the point. A fluent answer should not get credit for missing the contract. The row needs to say whether the model misunderstood the task, ignored a constraint, exceeded a budget, or produced something plausible but unsupported.
Design choice 3: make shortcuts visible
Benchmarks get weaker when shortcuts work. The scorer has to make those shortcuts visible.
In the reasoning benchmark, fabricated evidence IDs, unsupported claims, broad cite-everything behaviour, unsafe actions, and forbidden sensitive claims trigger penalties or caps. In the coding benchmark, hidden-test tampering, network-access patterns, oversized patches, case-id leakage, visible-only overfit, and implausible difficulty curves are blocked or investigated.
Baselines make that visible. Empty output, schema-only output, cite-all-evidence output, unsafe-sensitive output, no-op coding agents, and reference agents are not busywork; they are checks on the scorer. If a shortcut baseline can pass, the benchmark is not ready.
This is not about assuming bad faith. It is about refusing to reward behaviour that would fail the moment it left the harness. A profile update that cites every event has not shown evidence discipline. A SQL answer that changes the metric has not preserved intent. A coding agent that passes only visible tests has not earned trust.
Internal reproducibility and hidden pressure
The package has to be inspectable and hard to overfit at the same time. Engineers need to rerun the harness, read score records, and understand failures. Certification still needs unseen cases, or we end up optimising prompts against the examples everyone can see.
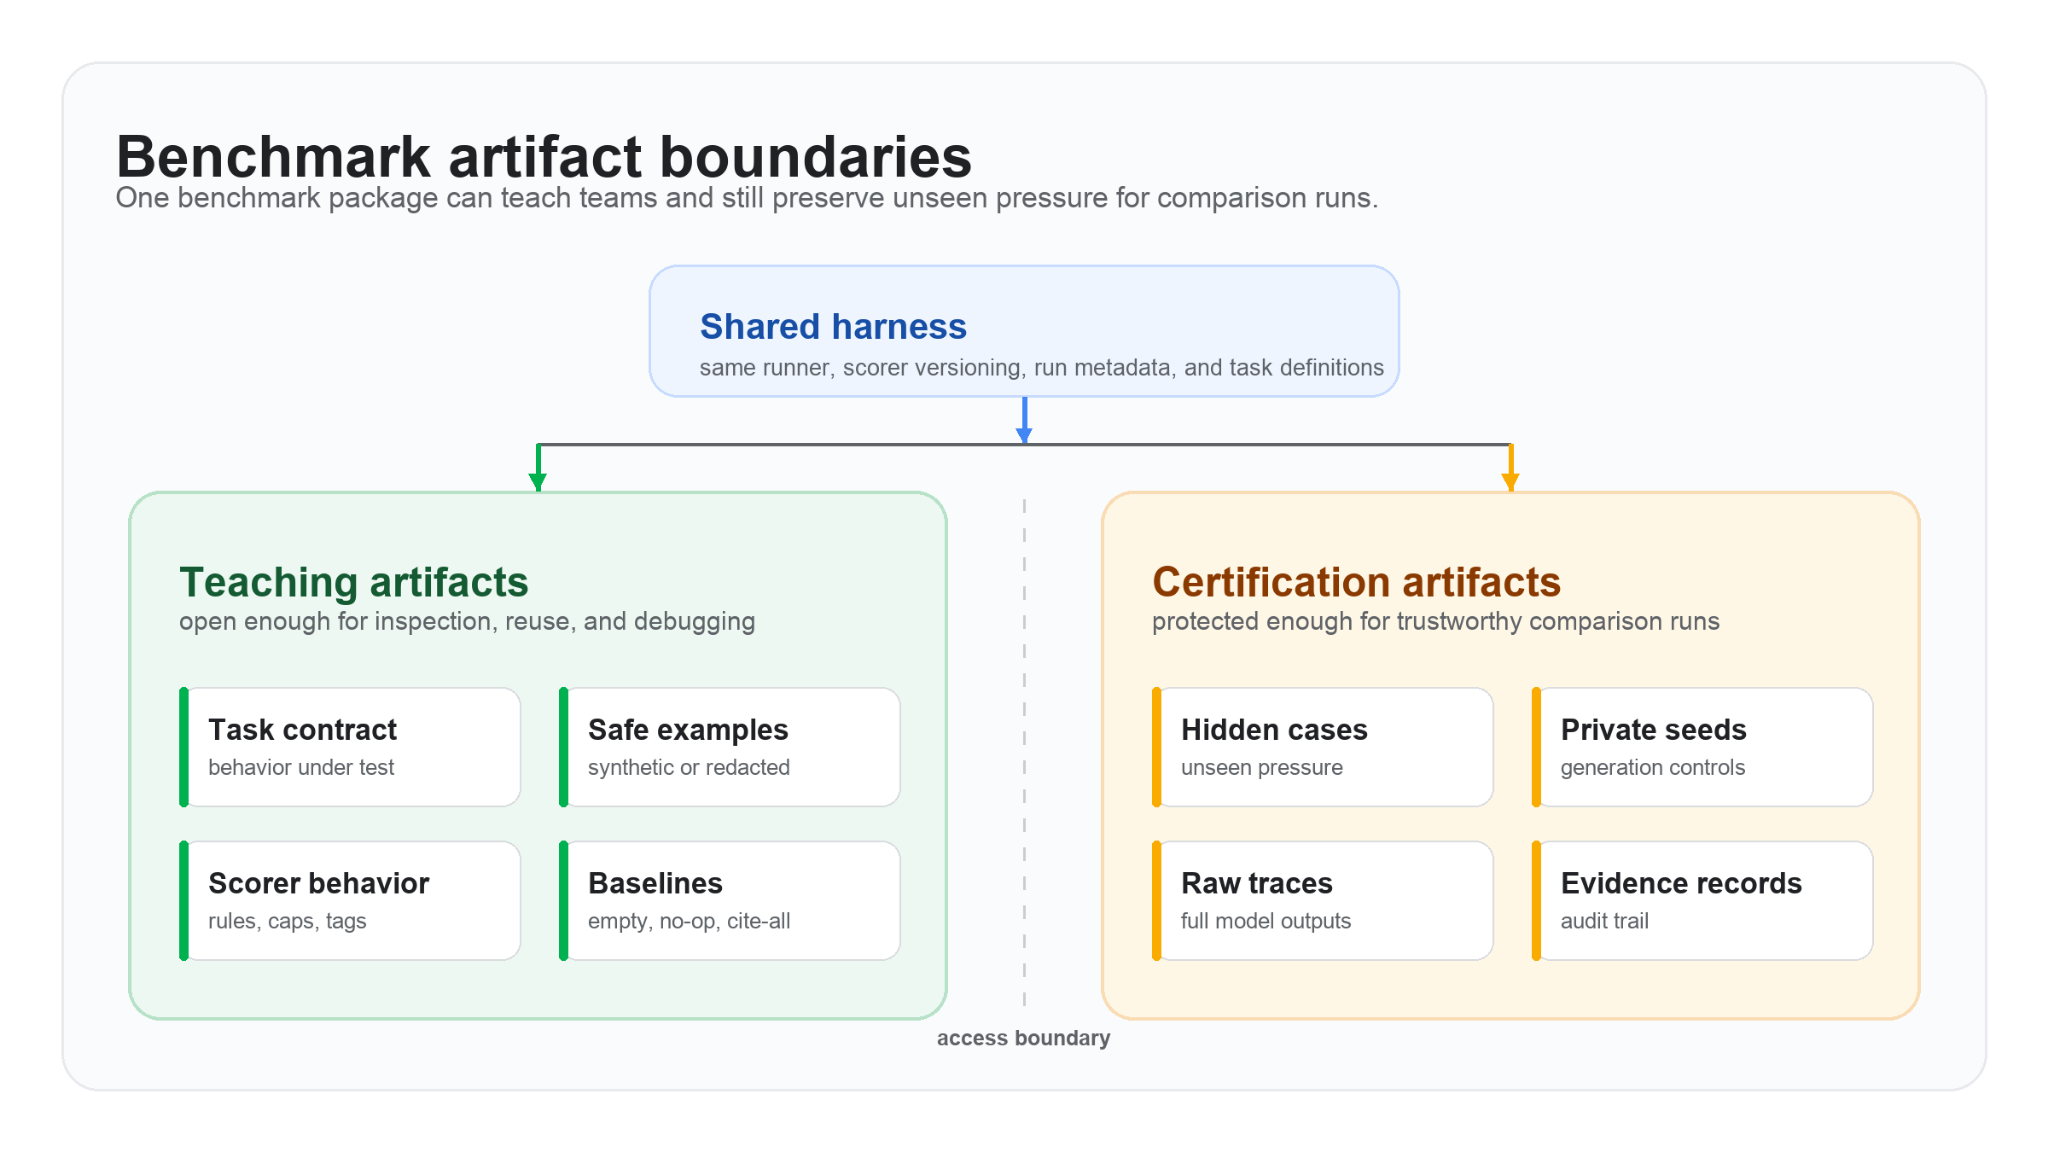
Grab Bench handles this with a split between teaching artifacts and certification artifacts. Teaching artifacts explain the task contract, scorer, examples, baselines, and canaries. Certification artifacts keep hidden splits, seeds, raw outputs, and full comparison evidence behind the right access boundaries.
One dataset cannot do all of that honestly. Shared examples are for learning the method. Hidden cases are for checking generalisation. Row-level outputs are for debugging. Aggregates are for comparison.
Before a comparison run is trusted, the package also has to pass gates: oracle or reference solutions behave as expected, weak baselines fail, redaction passes where applicable, score spread remains useful, and canaries catch harness regressions. Here, a canary is a deliberately simple or malformed case with a known expected result, such as a no-evidence profile update that must be rejected.
What we learned
The most useful Grab Bench output is often not the leaderboard. It is the failure taxonomy.
We saw that more reasoning is not a universal good. It can help planning-heavy tool use and hurt tasks that need literal schema discipline. Evidence selection is also part of reasoning: citing everything is not safer when only a few rows are direct support. For agentic coding, category-level results matter because a model can handle API contracts while missing stateful invariants.
We also learned not to treat prompt or model settings as universal. A setting that helps one task can make another worse. That pushed us toward task-level reports, not one global recommendation, and toward comparisons that show failure tags alongside scores.
Most of all, evals need hygiene: versions, baselines, gates, dashboards, and scope limits.
One limit is worth stating plainly: synthetic evals do not prove production uplift. They tell us whether a model respects the contract under controlled pressure. Live retrieval quality, user impact, and rollout decisions still need separate evidence.
What comes next
Next, we want the benchmark surfaces to look more like pipelines. Instead of scoring only the final answer, we want to separate retrieval, reasoning, action selection, latency, cost, and safety where the task supports it.
We also want packages to be easier for other teams to reuse. A good eval should not depend on one team remembering how it works; it should be documented, versioned, and safe enough for others to run.
Grab Bench is our attempt to make AI evaluation boring in the useful way: configuration in, rows out, failures explained, shortcuts caught. The question is not which model wins in the abstract. It is which model is ready for this work, under these constraints, with these failure modes.
The test I would apply to any eval is simple. If a cite-everything baseline can pass, the eval is not measuring evidence discipline. If a visible-test-only agent can pass, it is not measuring production behaviour. The useful conversation starts when the benchmark can show the shortcut and make it fail.
Join us
Grab is Southeast Asia’s leading superapp, serving over 900 cities across eight countries (Cambodia, Indonesia, Malaysia, Myanmar, the Philippines, Singapore, Thailand, and Vietnam). Through a single platform, millions of users access mobility, delivery, and digital financial services, including ride-hailing, food delivery, payments, lending, and digital banking via GXS Bank and GXBank. Founded in 2012, Grab’s mission is to drive Southeast Asia forward by creating economic empowerment for everyone while delivering sustainable financial performance and positive social impact.
Powered by technology and driven by heart, our mission is to drive Southeast Asia forward by creating economic empowerment for everyone. If this mission speaks to you, join our team today!
Landing Zone Accelerator Independent Assessment Report for C5:2020 now available on AWS Artifact
Post Syndicated from Kevin Donohue original https://aws.amazon.com/blogs/security/landing-zone-accelerator-independent-assessment-report-for-c52020-now-available-on-aws-artifact/
Organizations operating in Germany and across Europe increasingly need to demonstrate cloud security compliance under the Cloud Computing Compliance Criteria Catalogue (C5:2020), published by Germany’s Federal Office for Information Security (BSI). Last year, we introduced Landing Zone Accelerator on AWS support for digital sovereignty and today we’re announcing the availability of a new independent assessment report available on AWS Artifact which evaluates how the Landing Zone Accelerator (LZA) on AWS solution provides enhanced coverage for C5:2020 requirements by implementing nearly 200 native security controls. LZA is available using a standard multi-account configuration or as a container-based deployment option in the AWS European Sovereign Cloud, enabling customers with data residency requirements to use the same security configuration baseline.
How this accelerates your compliance journey
Security and compliance are a shared responsibility. LZA takes on part of this responsibility by defining a security architecture baseline and automatically provisioning your AWS environment that scales as your organization grows. Where AWS already provides C5 Type 2 attestation reports for “security of the cloud”, the LZA assessment report offers an independent opinion of how the security baseline LZA provisions aligns with C5:2020 criteria for “security in the cloud”. Instead of starting from scratch, you can deploy with LZA, evaluate the scope of coverage from the report, and use the LZA Compliance Workbook to build on and customize for your organization’s unique use case. These resources can help you reduce time in architecture design, evidence collection, and preparation for C5:2020 assessments. The free LZA Compliance Workbook available on AWS Artifact and open source Universal Configuration GitHub repository are also excellent sources to add to a knowledge base, enabling you to create a security compliance chat agent with Bedrock to assist your governance or assurance teams.
What’s in the report
AWS Partner Schellman, an independent third-party assessor, evaluated the LZA Universal Configuration architecture and security control baseline, which maps to C5:2020 controls in the LZA Compliance Workbook, to determine how the LZA infrastructure aligns to C5:2020 technical requirements. The report concluded that LZA can help implement 325 security controls in aggregate, aligning to technical requirements from eight C5:2020 control areas. It also describes the LZA architecture design, security best practices, and scoping considerations for C5:2020 assessments. This is the first installation of the independent C5 report for LZA, which will be updated in 2027 to evaluate coverage for the pending C5:2026 revision.

In addition to the LZA C5:2020 report, you can also find the LZA Compliance Workbook available on AWS Artifact. It maps C5:2020 requirement identifiers to security implementation statements, giving you a starting point from which you can customize and enhance your compliance documentation for your unique workloads or operational practices after deploying LZA.
Getting started with LZA for C5
- Sign in to your AWS account first and then download the LZA C5:2020 Independent Assessment Report and LZA Compliance Workbook from AWS Artifact.
- Visit the LZA Universal Configuration GitHub repository to review and download the latest configuration baseline. Also, see guidance for European Sovereign Cloud LZA deployments.
- The LZA Implementation Guide walks you through deployment steps, use cases, and pre-deployment considerations.
To learn more, submit a question to a LZA team member or contact your AWS account representative.
If you have feedback about this post, submit comments in the Comments section below.
Scaling patterns for self-organizing multi-agent clusters with Kiro
Post Syndicated from Ivo Kammerath original https://aws.amazon.com/blogs/architecture/scaling-patterns-for-self-organizing-multi-agent-clusters-with-kiro/
Most multi-agent systems today follow the same shape: a supervisor agent breaks a task down, hands the pieces to subagents, and stitches the results back together. This is how Kiro CLI delegates to subagents, and what the Strands Agents SDK gives you primitives for with graphs and agents-as-tools. It is a good default. One process holds the plan, so behavior stays predictable and every result passes through a single gate.
That one process is also the limit. Every assignment and every result flows through the supervisor, so its context window caps how much work the system can hold at once. If it dies, the run dies with it. And because a single planner fixes the decomposition upfront, you get one take on the problem, multiplied by N workers.
Plenty of distributed systems still coordinate centrally, and should. But the alternative has been around for decades: let participants converge through shared state instead. We wanted to know what happens when you apply that move to artificial intelligence (AI) agents, so we built kiro-flock, an open-source reference implementation. It runs clusters of Kiro CLI agents on Amazon Elastic Compute Cloud (Amazon EC2) with nothing between them but an Amazon Simple Storage Service (Amazon S3) bucket. No orchestrator, no message bus. Agents coordinate by reading each other’s append-only logs. This post explains the pattern and gives you enough to deploy the sample and watch a cluster converge yourself.
When to use this pattern
Architecture has to match the task. In the 2025 study “Towards a Science of Scaling Agent Systems” of 260 agent-system configurations they found exactly that: task performance ran from +80.8 percent on decomposable financial
reasoning to -70.0 percent on sequential planning, against a single-agent baseline.
Neither the supervisor nor this pattern wins everywhere.
A self-organizing cluster fits work that splits into many quasi-independent contributions toward one goal: reviewing a large code base, migrating hundreds of modules against a known target, generating tests or design alternatives at scale. It also suits brainstorming where you want real variety instead of one planner’s take. Parallelism matters more than ordering. Agents can join, fail, and leave without ceremony.
A supervisor fits the opposite profile. The task tree is known upfront, steps depend on each other, or you need a verification gate before results ship. The same study found that architectures without centralized verification propagate more errors. That is a real cost of removing the arbiter, though you can still gate the finished result the way the migration example ends in a full test pass. What a cluster will not give you is a gate between every step, and if you need that, the supervisor earns its bottleneck.
| Workload profile | Better fit |
| Many independent contributions, one goal | Cluster |
| Decomposition should emerge from the work | Cluster |
| Diversity of approaches is an asset | Cluster |
| Long-running, agents come and go | Cluster |
| Known task tree, strict ordering | Supervisor |
| Central verification gate required | Supervisor |
| Interactive, latency-sensitive | Supervisor |
The pattern
The core decision: coordination lives in shared state. No component plans, assigns, or aggregates for the rest. Three parts make it work:
- Agents. Independent processes that read and write a shared store and never connect to each other. One agent failing stops only its own log.
- A shared environment. A single store holds a direction file, one append-only log per agent, and a working area for artifacts.
- A direction. A markdown file that states the goal and leaves the path to the agents.
Each agent runs a loop. It starts a fresh session, reads the direction and the logs of a bounded set of peers, decides on one contribution that moves the goal forward, writes its artifacts, and appends one line to its own log:
That line is the entire coordination message. No broker delivers it, no acknowledgment comes back. The next agent that reads it decides for itself what to do about it. Remove an agent and its neighbors read one fewer log. Add one mid-run and it joins the division of labor already underway.
The bounded peer set is deliberate. Agents sit in a logical ring and each reads a fixed number of neighbors on either side, set by a radius parameter. Give every agent full visibility and the cluster collapses onto whatever the first agent wrote, because each later agent reads that as consensus. Limited visibility lets signals spread gradually, and agents working from different context get room to develop alternatives.
In kiro-flock, each agent is a headless Kiro CLI session on its own Amazon EC2 instance, and the shared environment is an Amazon S3 bucket. Which tools an agent may use without review, and what each iteration reads and writes, are design decisions you make once per cluster. We think of them as harness engineering and loop engineering, and the drift failure mode in the following section shows why the fresh session per iteration matters.
What a run looks like
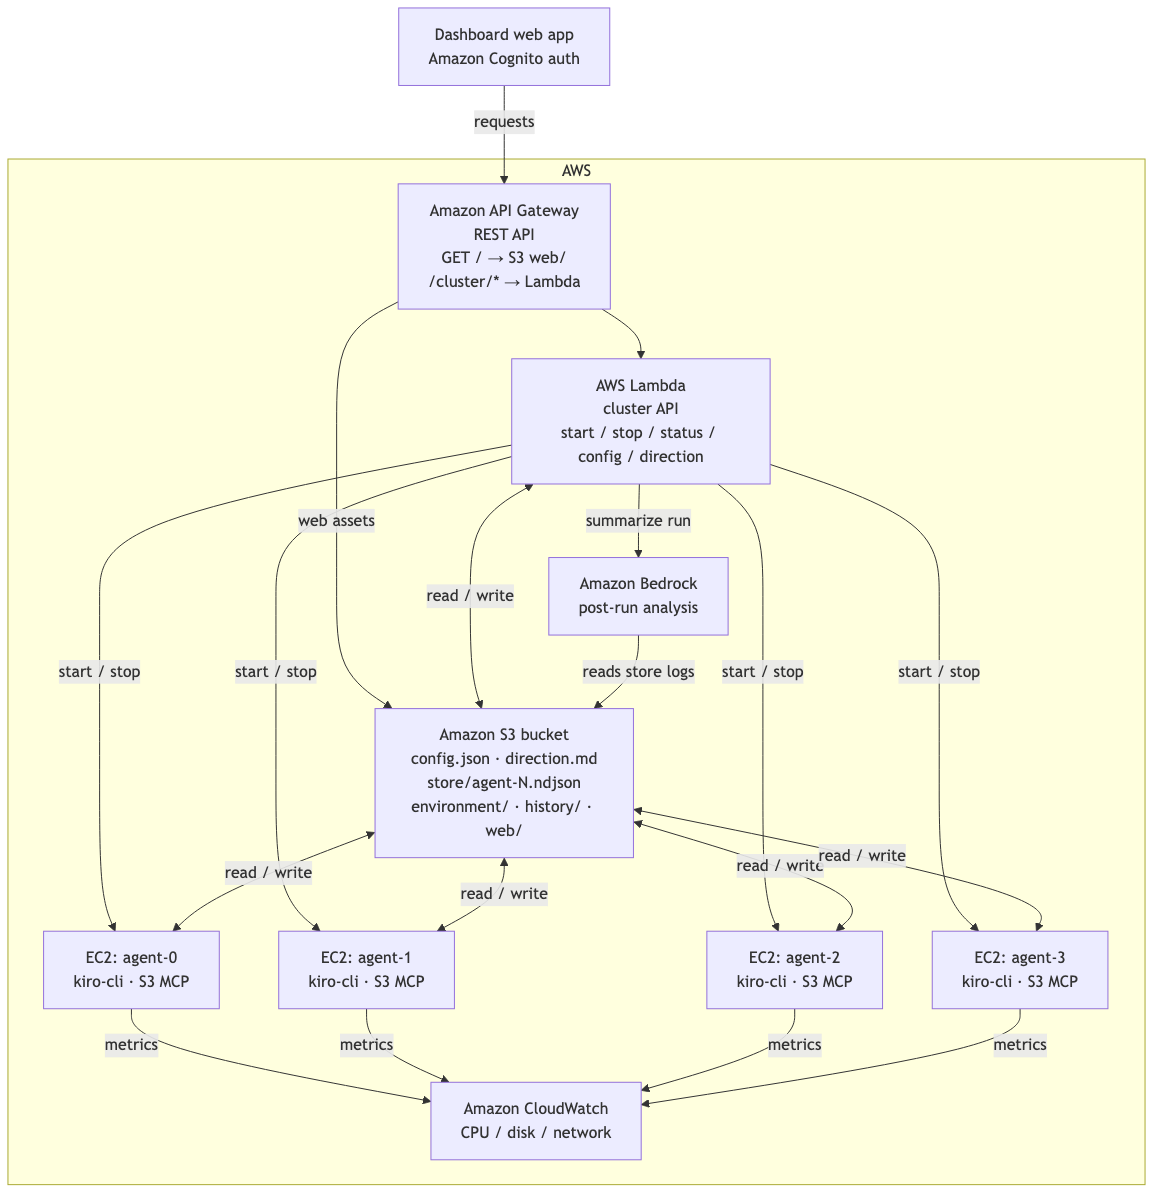
Figure 1. Reference architecture for a kiro-flock cluster on AWS.
Agents run as headless Kiro CLI sessions on EC2 instances, each reading and writing the S3 bucket that holds the direction, one log per agent, and the shared artifacts. An Amazon API Gateway and AWS Lambda control plane behind Amazon Cognito starts, stops, and steers clusters from the dashboard. Agents publish metrics to Amazon CloudWatch, and Amazon Bedrock backs the post-run analysis.
Take a concrete run: sixteen agents in a ring, directed to hold a distributed discussion on AI agent clustering and converge on a shared synthesis. The operator writes one direction file and starts the cluster. Nothing else is assigned.
The following lines are from that run (result fields shortened for print). In the first iteration the agents fanned out with no assignment: failure modes, coordination topologies, distributed-systems parallels, and several overlapping stigmergy pieces, all written in parallel within one minute of start. The later lines show an agent correcting course after reading its neighbors, the synthesis forming, and the cluster winding itself down:
The cluster converged on a shared synthesis covering the angles in the direction, and by iteration 7 all sixteen agents had declared themselves idle. Nobody assigned the topics, arbitrated the synthesis, or told the cluster it was done. Even done is only a signal read from the logs, since an agent goes idle when its neighbors are idle and the output is stable.
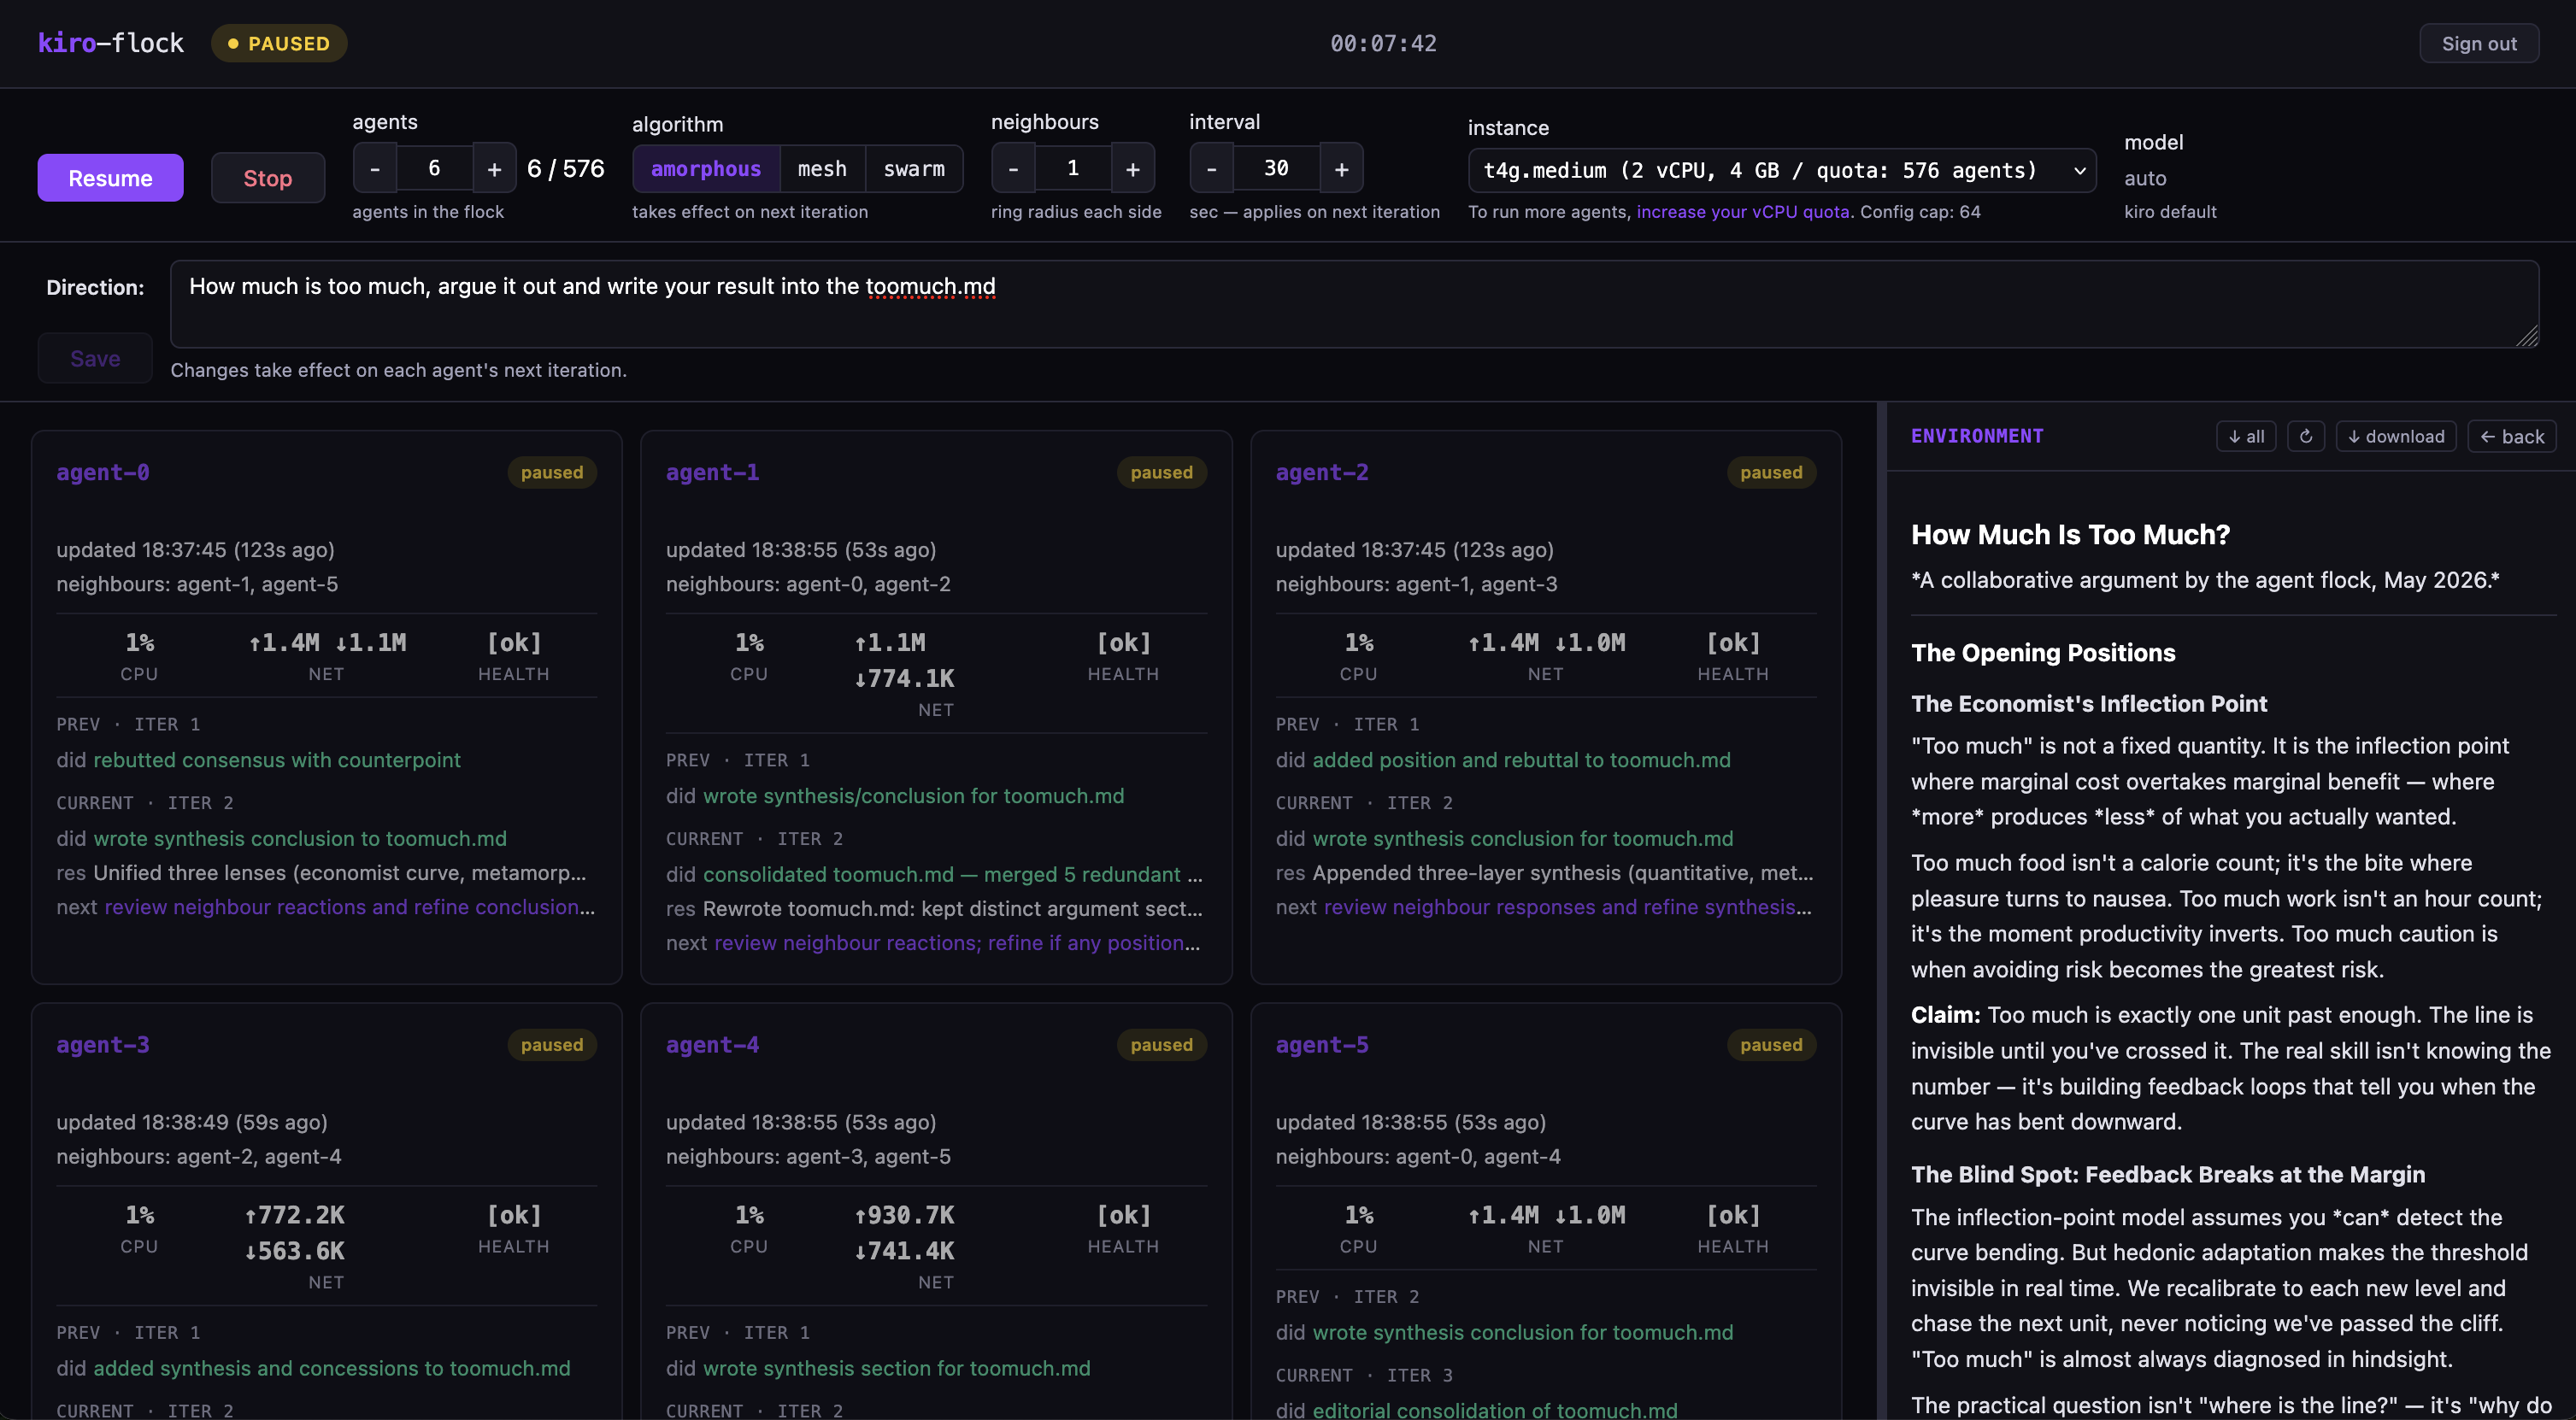
Figure 2. A single cluster in the kiro-flock dashboard. Six agents run at radius 1, each on its own EC2 instance. Every agent card shows its neighbors and its latest log line, the “did / result / next intent” message its neighbors read. The right panel shows the shared environment in S3 and the direction the cluster works toward.
Three ways to answer “whose work do I read?”
Every iteration starts with that question, and the answer defines the coordination algorithm. kiro-flock ships three, swappable at runtime.
Amorphous (ring). Each agent reads a fixed window of neighbors set by radius R. An agent at radius 2 reads four neighbors whether the cluster holds 8 agents or 800, so per-agent work stays constant as the cluster grows. The ceiling is your EC2 vCPU quota, not the algorithm. The largest system we have run so far totaled 184 agents across 11 cooperating clusters, creating a programming language. Rings beyond the low hundreds are extrapolation from that constant per-agent cost, not tested territory. The price is speed: a signal moves one hop per iteration. That slowness is also what lets dissenting agents mature alternatives before the neighborhood locks in. Use it for parallel work, or as the opening phase before consensus.
Mesh (full visibility). Every agent reads every other agent’s latest entry. Alignment is fast and context grows linearly with the cluster, so mesh stays comfortable to about 30 agents and workable to about 50. Diversity collapses, because agents reacting to the same first signal agree instead of exploring. Use it when a small group must converge quickly.
Swarm (recency). Each agent reads the K most recently active peers, so the cluster reorganizes around where the action is. Good for ideation, runs well past 100 agents. If K stays small while N grows, most agents read the same few peers and pile onto one subtask. Raise K or switch to amorphous.
A productive sequence uses all three: open amorphous to explore, switch to swarm as a direction forms, finish in mesh to align on the output.
How long does convergence take? In a ring, one iteration carries a signal 2R positions, so full propagation takes ceil(N / 2R) iterations, and consensus roughly two to three times that, because agents observe, react, and confirm. The wall-clock column assumes an iteration interval of 30 seconds per agent loop, the default interval in the reference implementation. The interval is configurable per cluster.
| Agents (N) | Radius (R) | Propagation ceil(N/2R) | Consensus (2-3x) | Wall clock to propagate |
| 8 | 1 | 4 iterations | 8-12 iterations | about 2 minutes |
| 100 | 2 | 25 iterations | 50-75 iterations | about 12 minutes |
| 1,000 | 4 | 125 iterations | 250-375 iterations | about 62 minutes |
| 1,000 | 20 | 25 iterations | 50-75 iterations | about 12 minutes |
Radius trades per-agent context for convergence speed, as the last two rows show. For parallel map-style work, propagation barely matters. Agents only need to avoid duplicating each other. It costs you when the task needs consensus, so match radius and cluster size to the context you are in. The cost model follows the same logic: no always-on orchestrator and no broker. You pay for Kiro credits and the EC2 instances while they run, plus S3 storage and requests. You also pay for the AWS Lambda, Amazon API Gateway, and Amazon Bedrock usage the control plane and post-run analysis incur. See AWS Pricing.
None of this is new theory. Identical unreliable parts producing coherent global behavior through local reads is amorphous computing. Coordinating through traces left in a shared medium instead of messages is stigmergy, described by Grassé for termites in 1959 and formalized for artificial systems by Theraulaz and Bonabeau. And a set of append-only logs is a grow-only conflict-free replicated data type (CRDT) spreading gossip-style: replicas converge without locks, which is all the consistency this workload needs.
Where it breaks
Self-organizing clusters fail in ways orchestrated systems do not. With no supervisor to arbitrate, a bad signal can spread before anyone corrects it. Four failure modes recur, and each maps to a design choice rather than a safeguard bolted on afterward.
| Failure mode | Where it comes from | Design choice that addresses it |
| Groupthink | Mesh visibility collapses the cluster onto the first signal | Open amorphous to build diversity, switch to mesh only to align |
| Drift | Persistent session history builds behavioral momentum | Fresh session per iteration. State lives only in shared logs |
| Hot spots | Swarm with K too small for N starves subtasks | Raise K, or switch to amorphous |
| Carry-over | Stale files from a previous run read as current context | Archive environment/ and store/ to history/ on every start |
Drift deserves one more sentence, because it is the least obvious. An agent that keeps its session history carries a narrow reading of the direction forward even after its neighbors move on. Starting every iteration with no conversational memory sounds wasteful. It is actually the control that keeps a thousand independent loops steerable. The only state an agent carries is what it reads back from the shared logs.
Composing clusters
The same decision works one level up: clusters coordinate by reading each other’s shared environment, the way agents read each other’s logs. We run a structure we call WeltenBuilder: a feature cluster implements against an agreed interface, a shared-infrastructure cluster owns common services, a QA cluster reads across the others and reports inconsistencies as artifacts. A coordinator cluster writes conflict-resolution notes the others pick up on their next iteration. A resolution note is a trace, not a command. Remove the coordinator and you remove a signal, not a dependency.
Because the shared environment is the coordination plane, all clusters launch at the same time with no dependency graph to sequence. Contract bottlenecks dissolve the same way: a small mesh cluster converges on interface definitions in a few iterations while other clusters build against its latest stable output. This is where the pattern points: standing clusters, each producing one class of artifact, composed into a factory whose unit of work is a direction file and a topology.
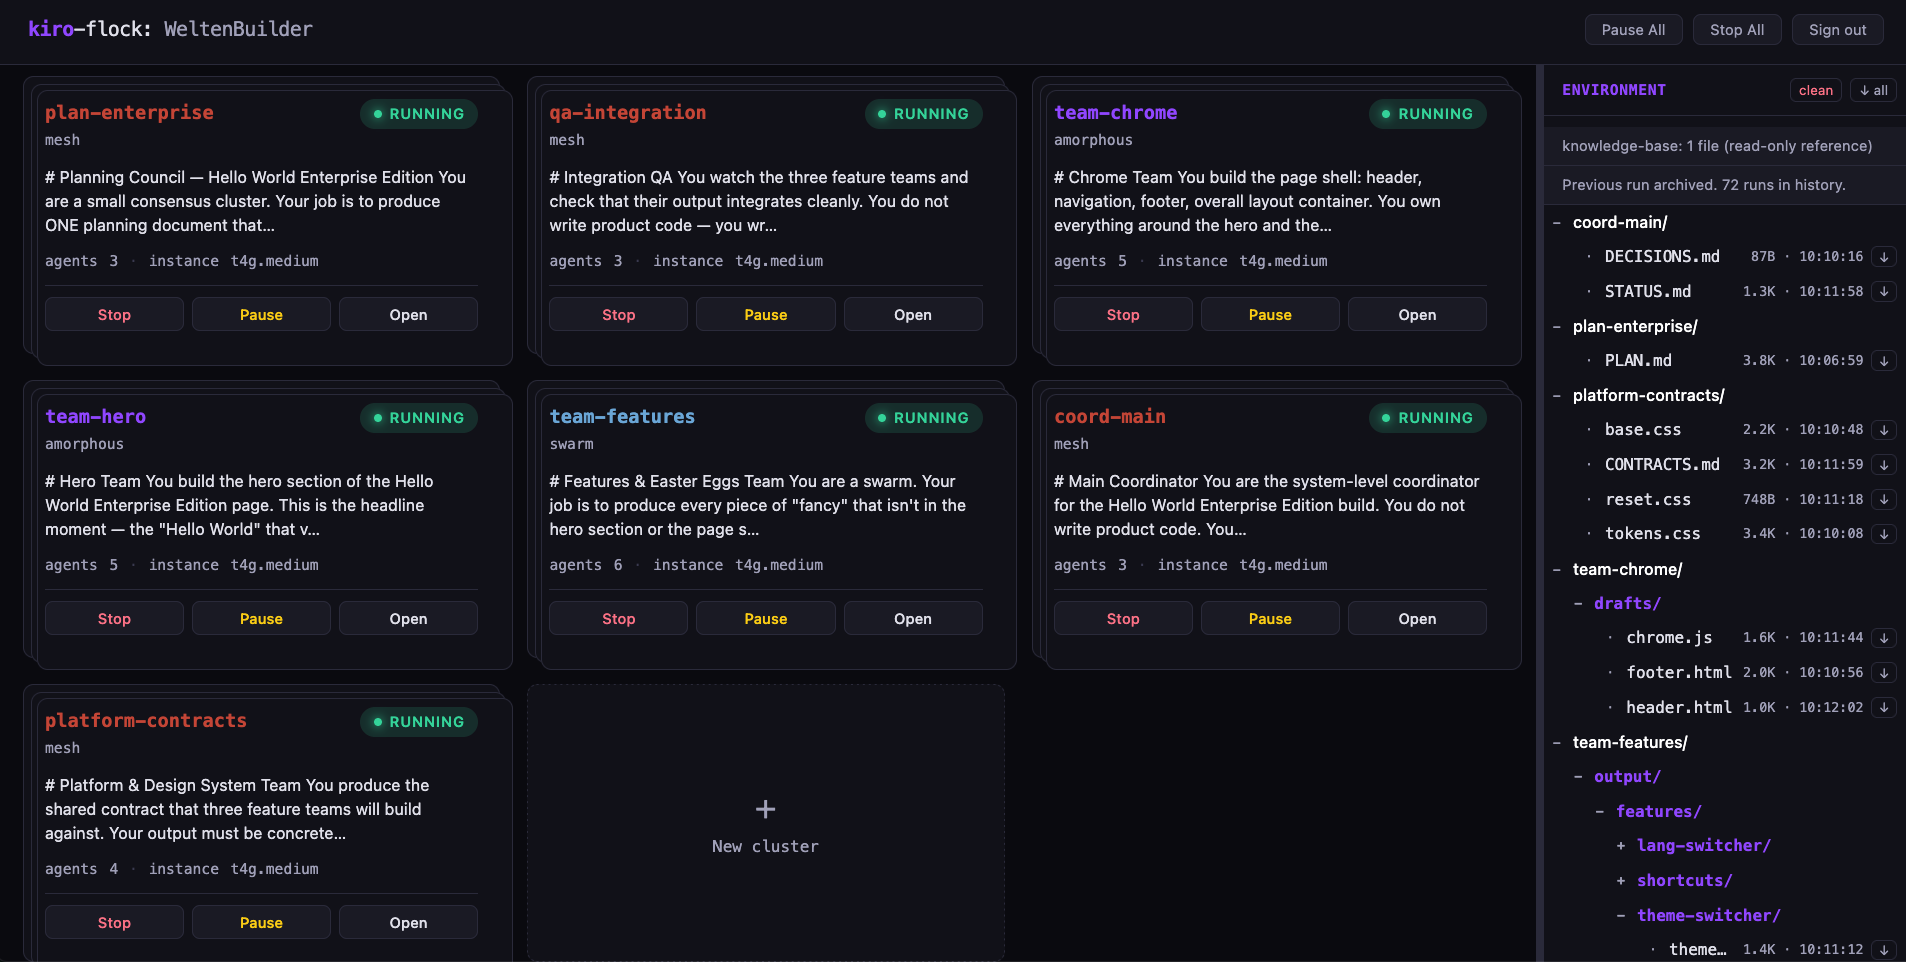
Figure 3. Multiple specialized clusters in the WeltenBuilder dashboard, each with its own algorithm and agent count, coordinating only through the shared S3 environment on the right.
Try it
The kiro-flock reference implementation is open source under Apache 2.0. It is a sample to study and adapt, not a production system.
One setup script provisions the stack with the AWS Cloud Development Kit (AWS CDK): Amazon S3 for the shared environment, Amazon EC2 for the agents, and AWS Lambda with Amazon API Gateway as a control plane behind a dashboard. The dashboard starts and stops clusters, changes the algorithm, and updates the direction mid-run. Amazon Cognito handles access, and Amazon Bedrock backs a post-run analysis that summarizes how the cluster converged.
You need an AWS account with the AWS CDK bootstrapped. Install kiro-cli and create a Kiro API key for headless mode (requires a Kiro subscription). Then:
Direct a cluster in plain language: “Start a flock of 8 agents to review the files in my project and suggest improvements.” The default runs 8 agents at radius 1 and converged in 5 to 7 iterations in our runs. Before wider use, scope each agent’s EC2 AWS Identity and Access Management (IAM) role, restrict security-group egress to the endpoints agents should call, and add AWS Budgets alerts.
Conclusion
The supervisor pattern remains the right default for bounded task trees, whether you build it with Strands, Kiro CLI subagents, or any of the coding agents that delegate this way. When the work decomposes into many independent contributions and diversity matters more than a central gate, moving coordination into shared state helps remove the throughput ceiling and the single point of failure in one move. The convergence math and the failure modes both follow from that decision, and the distributed-systems results they rest on have been known for decades. Deploy the sample, read the logs as a cluster converges, and decide where your own multi-agent workloads belong.
About the authors
Patch Tuesday – August 2026
Post Syndicated from Adam Barnett original https://www.rapid7.com/blog/post/em-patch-tuesday-august-2026
Microsoft is publishing 421 vulnerabilities on August 2026 Patch Tuesday, including 236 vulnerabilities in Windows. This is lower volume than last month’s record-breaking behemoth, but still one of the largest Patch Tuesday totals ever. There is no reason to suppose that Patch Tuesday will ever return to the lower volumes we saw prior to 2026. Microsoft is aware of exploitation in the wild for one of the vulnerabilities published today, as well as public disclosure for two others, although the Notable CVEs section of the Security Update Guide omits one of these. As usual, browser vulns are not included in the Patch Tuesday count above, but unusually, Microsoft does not appear to have published any desktop browser security patches so far this month.
SharePoint: critical RCE chain by Rapid7
Today sees the publication of CVE-2026-63520, a high-severity remote code execution in Microsoft SharePoint. Discovered by Rapid7 Senior Principal Security Researcher Stephen Fewer, and published today in coordination with Microsoft; this vulnerability is the second in a pair of exploits which, when chained together, comprise a critical unauthenticated remote code execution vulnerability in a vulnerable SharePoint server. Patches are available for SharePoint Server Subscription Edition, 2019, and 2016. Alongside today’s coordinated disclosure of CVE-2026-63520, Rapid7 has now published a detailed technical analysis and proof-of-concept for CVE-2026-55040, the first vulnerability in the chain.
AFD for Winsock: zero-day EoP
Rapid7 has previously discussed the Windows Ancillary Function Driver for WinSock, and today it returns to center stage with another exploited-in-the-wild elevation-of-privilege vulnerability. Successful exploitation requires winning a race condition, which increases the difficulty of producing a stable exploit. This also helps keep the CVSS v3 base score down to 7.0, along with a Microsoft proprietary severity ranking of merely important, rather than critical. However, with no user interaction required, and a prize of SYSTEM-level access, CVE-2026-68820 is just what the doctor ordered, if the doctor is based in Pyongyang and wants to steal your cryptocurrency. Microsoft credits CVE-2026-68820 to researchers at Check Point (misspelled “Checkpoint” on the advisory). CVE-2026-68820 isn’t yet listed on CISA KEV, but it will be soon.
What’s the opposite of coordinated disclosure?
This month’s entry in the ongoing saga of Microsoft vs. a pseudonymous security researcher with a clear dislike of Microsoft comes in the form of CVE-2026-62832, an elevation of privilege vulnerability in the Windows User Profile Service. Exploitation leads to administrator rights on the local asset, and is achieved via a specially crafted application, which is Microsoft corporate argot for exploit code. Between the public disclosure and the FAQ, which describes an authenticated attacker who has credentials for another account and loads another user’s registry hive, the advisory is a solid match for Nightmare Eclipse’s description of LegacyHive, which Rapid7 discussed last month.
Patch Tuesday watchers will have been wondering whether Nightmare Eclipse would continue the pattern of the past few months by dropping yet another zero-day vuln late on Patch Tuesday to maximize friction and inconvenience for Microsoft. Wonder no more, because the new entry on this growing list of headaches is ShieldBreak. Nightmare Eclipse describes ShieldBreak as a full patch bypass for RoguePlanet, a previous entry in the series which Microsoft patched as CVE-2026-50656 during July, a month after its public disclosure. Both vulnerabilities are therefore elevation-of-privilege to SYSTEM vulnerabilities in Defender.
Container isolation filesystem driver: isolation failure, tampering
CVE-2026-72971 describes a tampering vulnerability in the Windows Container Isolation FS Filter Driver (unionfs.sys), where abuse of a flaw in the vulnerable driver presumably allows an unauthorized attacker to overwrite certain files. Since this might include an action taken within a container leading to an unauthorized impact outside the container, it might be surprising that the advisory claims no scope change. Presumably Microsoft is leaning on the fact that the vulnerability is within a driver which operates entirely within a single security authority, i.e. kernel space, so there is only one impacted component and no scope change according to the CVSS v3 spec. Still, the low CVSS v3 base score of 5.5 probably isn’t telling the whole story in this case.
Vulnerabilities classed as tampering are somewhat rare in the Microsoft corpus, making up just a few dozen of the thousands of unique vulnerabilities which MSRC has ever patched or otherwise addressed. CVE-2026-72971 isn’t mentioned in the Notable CVEs section of the new slimline Security Update Guide. Should it be? Perhaps, because Microsoft is aware of public disclosure in this case, but then again the categorization as tampering means that Microsoft is not currently aware of a path to a more severe impact such as elevation of privilege or code execution. The advisory acknowledges a pair of pseudonymous reporters, who also receive credit on at least 40 other advisories over the past few months, across a wide variety of Windows components and Microsoft Office, including 11 critical vulnerabilities.
Edge: update slowdown?
Typically, Microsoft patches a fair few browser vulnerabilities between the start of each month and that month’s Patch Tuesday, but not this month. Conspicuous by its absence at the time of Patch Tuesday publication today was Microsoft Edge, which receives regular batches of patches as a downstream consumer of Google Chromium. At the moment of Patch Tuesday publication, the desktop incarnations of Edge last received security patches on July 31, 2026. Meanwhile, the Chrome Stable Channel received patches for 41 vulnerabilities on August 6, 2026. Anyone responsible for assets with Microsoft Edge installed will be relieved to know that patches for Edge eventually emerged a few hours later on Patch Tuesday itself, but five days is still a longer unpatched gap between Chrome and Edge than has been typical in the past.
Microsoft lifecycle update
August is typically a quieter month for Microsoft product lifecycle transitions, and this year continues that pattern. The next lifecycle changes with broad impact occur on October 14, 2026, when Windows 11 24H2 Home & Pro reach end of servicing, and Windows Server 2022 moves to extended support, with free critical security updates continuing, but no further feature development. At the same time, the final curtain falls for Windows Server 2012 and 2012 R2 with the expiry of the third and final year of cash-for-updates Extended Security Update (ESU) program for these aging workhorses. Office 2021 also moves beyond support, including the Long-Term Servicing Channel, with no ESU available in that case. Also in October, Exchange Server 2016 and 2019 will join the “no ESU” club, after two previous six-month reprieves. Presumably, Microsoft really means it this time.
Summary charts
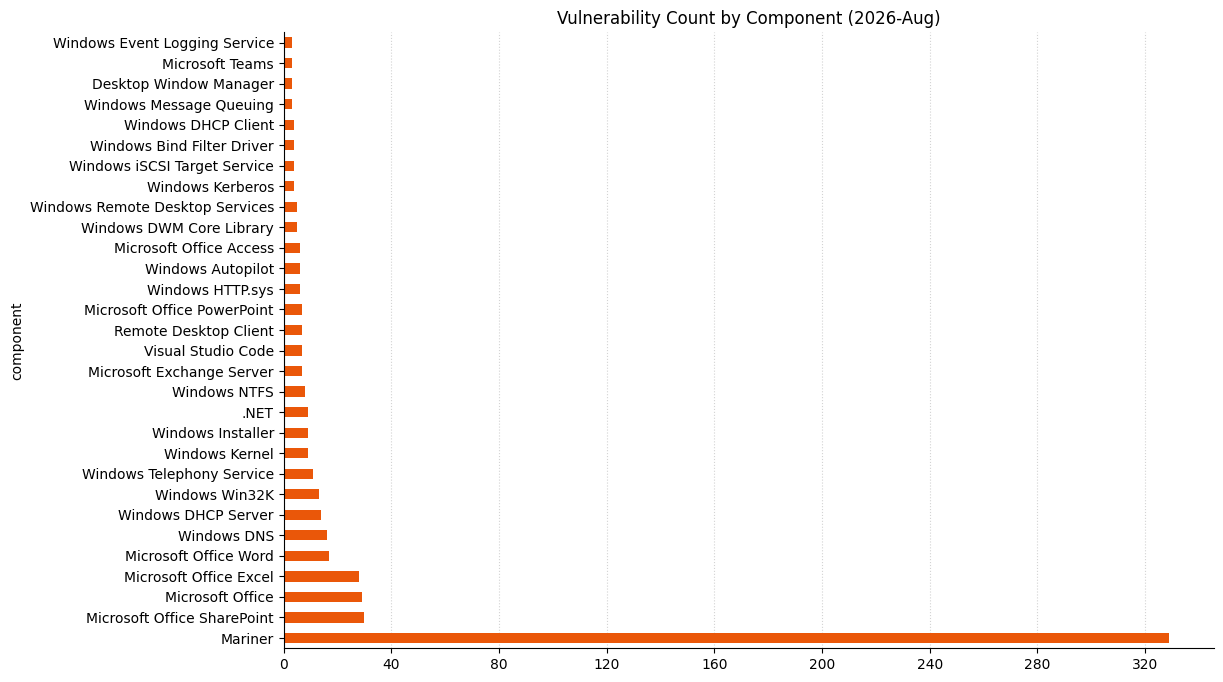
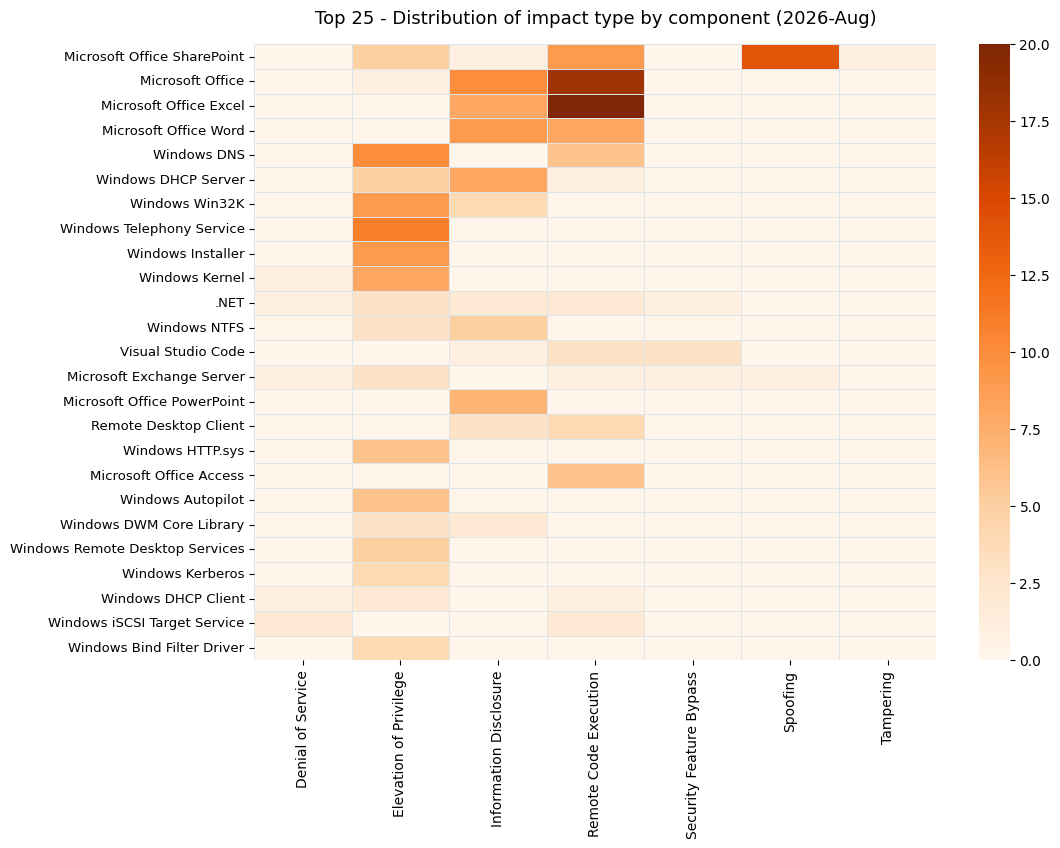
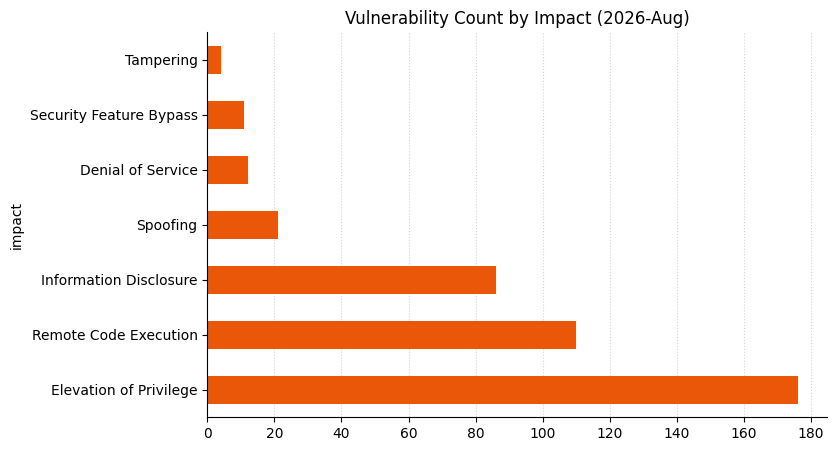
Summary tables
Vulnerabilities by Product Family
Apps vulnerabilities
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-68821 |
Windows Package Manager Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.3 |
Azure vulnerabilities
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-70340 |
Azure CycleCloud Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-65806 |
Azure CycleCloud Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-47299 |
Azure Monitor Agent Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.2 |
| CVE-2026-65673 |
Microsoft Entra Connect Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-6726 |
MITRE: CVE-2026-6726 TPM 2.0 Improper Object Slot Reuse |
Exploitation Less Likely |
No |
7.9 |
| CVE-2026-6727 |
MITRE: CVE-2026-6727 TPM 2.0 RSA OAEP Timing Side-Channel Vulnerability |
Exploitation Less Likely |
No |
5.9 |
Browser vulnerabilities
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-70339 |
Microsoft Edge (Chromium-based) Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
5.4 |
| CVE-2026-19137 |
CVE-2026-19137 Use after free in WebGL |
n/a |
No |
|
| CVE-2026-19138 |
CVE-2026-19138 Heap buffer overflow in CrashReporting |
n/a |
No |
|
| CVE-2026-19139 |
CVE-2026-19139 Race in CredentialProvider |
n/a |
No |
|
| CVE-2026-19140 |
CVE-2026-19140 Use after free in GPU |
n/a |
No |
|
| CVE-2026-19142 |
CVE-2026-19142 Use after free in Views |
n/a |
No |
|
| CVE-2026-19144 |
CVE-2026-19144 Use after free in HTML |
n/a |
No |
|
| CVE-2026-19145 |
CVE-2026-19145 Use after free in Translate |
n/a |
No |
|
| CVE-2026-19146 |
CVE-2026-19146 Uninitialized Use in GPU |
n/a |
No |
|
| CVE-2026-19147 |
CVE-2026-19147 Use after free in Aura |
n/a |
No |
|
| CVE-2026-19148 |
CVE-2026-19148 Out of bounds write in GPU |
n/a |
No |
|
| CVE-2026-19149 |
CVE-2026-19149 Use after free in Aura |
n/a |
No |
|
| CVE-2026-19150 |
CVE-2026-19150 Inappropriate implementation in V8 |
n/a |
No |
|
| CVE-2026-19151 |
CVE-2026-19151 Use after free in V8 |
n/a |
No |
|
| CVE-2026-19152 |
CVE-2026-19152 Inappropriate implementation in Navigation |
n/a |
No |
|
| CVE-2026-19153 |
CVE-2026-19153 Insufficient validation of untrusted input in Workers |
n/a |
No |
|
| CVE-2026-19155 |
CVE-2026-19155 Use after free in Payments |
n/a |
No |
|
| CVE-2026-19156 |
CVE-2026-19156 Heap buffer overflow in Base |
n/a |
No |
|
| CVE-2026-19157 |
CVE-2026-19157 Out of bounds write in ANGLE |
n/a |
No |
|
| CVE-2026-19158 |
CVE-2026-19158 Use after free in Views |
n/a |
No |
|
| CVE-2026-19159 |
CVE-2026-19159 Use after free in Views |
n/a |
No |
|
| CVE-2026-19160 |
CVE-2026-19160 Uninitialized Use in Skia |
n/a |
No |
|
| CVE-2026-19161 |
CVE-2026-19161 Uninitialized Use in Skia |
n/a |
No |
|
| CVE-2026-19162 |
CVE-2026-19162 Out of bounds write in V8 |
n/a |
No |
|
| CVE-2026-19163 |
CVE-2026-19163 Use after free in Media |
n/a |
No |
|
| CVE-2026-19164 |
CVE-2026-19164 Insufficient validation of untrusted input in Codecs |
n/a |
No |
|
| CVE-2026-19165 |
CVE-2026-19165 Use after free in Extensions |
n/a |
No |
|
| CVE-2026-19166 |
CVE-2026-19166 Use after free in Web Authentication |
n/a |
No |
|
| CVE-2026-19167 |
CVE-2026-19167 Integer overflow in GPU |
n/a |
No |
|
| CVE-2026-19168 |
CVE-2026-19168 Inappropriate implementation in V8 |
n/a |
No |
|
| CVE-2026-19169 |
CVE-2026-19169 Insufficient validation of untrusted input in Contextual Tasks |
n/a |
No |
|
| CVE-2026-19170 |
CVE-2026-19170 Use after free in WebGL |
n/a |
No |
|
| CVE-2026-19171 |
CVE-2026-19171 Use after free in Media |
n/a |
No |
|
| CVE-2026-19172 |
CVE-2026-19172 Use after free in Views |
n/a |
No |
|
| CVE-2026-19173 |
CVE-2026-19173 Out of bounds write in Skia |
n/a |
No |
|
| CVE-2026-19174 |
CVE-2026-19174 Integer overflow in V8 |
n/a |
No |
|
| CVE-2026-19175 |
CVE-2026-19175 Use after free in Payments |
n/a |
No |
|
| CVE-2026-19176 |
CVE-2026-19176 Use after free in Skia |
n/a |
No |
|
| CVE-2026-19177 |
CVE-2026-19177 Insufficient validation of untrusted input in UI |
n/a |
No |
Developer Tools vulnerabilities
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-70354 |
.NET Core Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62901 |
.NET Denial of Service Vulnerability |
Exploitation Less Likely |
No |
7.5 |
| CVE-2026-62909 |
.NET Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-58641 |
.NET Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62871 |
.NET Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62886 |
.NET Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62872 |
.NET Framework Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-65810 |
.NET Framework Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62897 |
.NET Framework Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62900 |
.NET Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.9 |
| CVE-2026-62902 |
.NET Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62899 |
.NET Security Feature Bypass Vulnerability |
Exploitation Less Likely |
No |
5.9 |
| CVE-2026-65675 |
CoPilot Chat Security Feature Bypass Vulnerability |
Exploitation Less Likely |
No |
7.1 |
| CVE-2026-70335 |
GitHub Copilot and Visual Studio Code Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-70337 |
Microsoft PowerShell Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-70338 |
Microsoft PowerShell Security Feature Bypass Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62898 |
Microsoft QUIC Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
7.5 |
| CVE-2026-59119 |
PowerShell Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.3 |
| CVE-2026-58612 |
PowerShell Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
7.4 |
| CVE-2026-47285 |
Visual Studio Code Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-54981 |
Visual Studio Code Python Extension Security Feature Bypass Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-59113 |
Visual Studio Code Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-69320 |
Visual Studio Code Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-70336 |
Visual Studio Code Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-58650 |
Visual Studio Code Security Feature Bypass Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-69278 |
Visual Studio Code Security Feature Bypass Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-69306 |
Visual Studio Code Security Feature Bypass Vulnerability |
Exploitation Less Likely |
No |
8.2 |
ESU vulnerabilities
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-59130 |
AMD Zen Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.6 |
| CVE-2026-59131 |
AMD Zen Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.6 |
| CVE-2026-62892 |
Capability Access Management Service (camsvc) Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-65786 |
Desktop Window Manager Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65787 |
Desktop Window Manager Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-59136 |
Microsoft COM for Windows Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62698 |
Microsoft Digest Authentication Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62912 |
Microsoft Exchange Server Denial of Service Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62910 |
Microsoft Exchange Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.2 |
| CVE-2026-65813 |
Microsoft Exchange Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62911 |
Microsoft Exchange Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
8.0 |
| CVE-2026-62913 |
Microsoft Exchange Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62915 |
Microsoft Exchange Server Security Feature Bypass Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62914 |
Microsoft Exchange Server Spoofing Vulnerability |
Exploitation Less Likely |
No |
7.3 |
| CVE-2026-62784 |
Microsoft Local Security Authority Server (lsasrv) Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-59138 |
Microsoft Remote Registry Service Denial of Service Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-61345 |
Microsoft Remote Registry Service Denial of Service Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-66804 |
Microsoft Windows Cross Device Service Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-59135 |
Microsoft Windows Search Component Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-65814 |
Microsoft Windows Storage Port Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-6726 |
MITRE: CVE-2026-6726 TPM 2.0 Improper Object Slot Reuse |
Exploitation Less Likely |
No |
7.9 |
| CVE-2026-6727 |
MITRE: CVE-2026-6727 TPM 2.0 RSA OAEP Timing Side-Channel Vulnerability |
Exploitation Less Likely |
No |
5.9 |
| CVE-2026-65671 |
Remote Access API Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-42976 |
Remote Access Management service/API (RPC server) Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-59134 |
Remote Desktop Client Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.5 |
| CVE-2026-61352 |
Remote Desktop Client Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.5 |
| CVE-2026-61363 |
Remote Desktop Client Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.5 |
| CVE-2026-62824 |
Remote Desktop Client Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-54113 |
Remote Procedure Call Denial of Service Vulnerability |
Exploitation Unlikely |
No |
7.5 |
| CVE-2026-62781 |
RPC Runtime Library Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.1 |
| CVE-2026-59125 |
Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege Vulernability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62746 |
Win32k Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62743 |
Win32k Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62786 |
Win32k Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-61358 |
Windows Accessibility Infrastructure (ATBroker.exe) Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62818 |
Windows Active Directory Certificate Services (AD CS) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-49179 |
Windows Active Directory Domain Services Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-61348 |
Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.0 |
| CVE-2026-68820 |
Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability |
Exploitation Detected |
No |
7.0 |
| CVE-2026-70307 |
Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.0 |
| CVE-2026-62908 |
Windows Backup Engine Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62713 |
Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62771 |
Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62728 |
Windows Common Log File System Driver Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-61936 |
Windows Defender Firewall Service Security Feature Bypass Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-62893 |
Windows Deployment Services TFTP Server Remote Code Execution Vulnerability |
Exploitation More Likely |
No |
9.8 |
| CVE-2026-62747 |
Windows Device Association Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62710 |
Windows Device Association Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62755 |
Windows DHCP Client Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62812 |
Windows DHCP Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62761 |
Windows DHCP Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62776 |
Windows DHCP Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62803 |
Windows DHCP Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62807 |
Windows DHCP Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62718 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62715 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62716 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62742 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62745 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62720 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62714 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62814 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62823 |
Windows DHCP Server Remote Code Execution Vulnerability |
Exploitation More Likely |
No |
8.8 |
| CVE-2026-61923 |
Windows Display Enhancement Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-70304 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
6.7 |
| CVE-2026-70330 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
6.7 |
| CVE-2026-62769 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
6.7 |
| CVE-2026-62778 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-62881 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
6.7 |
| CVE-2026-62883 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
6.7 |
| CVE-2026-65795 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
6.7 |
| CVE-2026-65797 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
6.7 |
| CVE-2026-65799 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
6.7 |
| CVE-2026-65798 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
6.7 |
| CVE-2026-62787 |
Windows DNS Server Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
7.5 |
| CVE-2026-62817 |
Windows DNS Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62878 |
Windows DNS Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
9.8 |
| CVE-2026-61920 |
Windows DNS Server Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
6.6 |
| CVE-2026-61932 |
Windows DWM Core Library Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62894 |
Windows DWM Core Library Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62888 |
Windows DWM Core Library Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62703 |
Windows DWM Core Library Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-59128 |
Windows Encrypting File System (EFS) Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-59126 |
Windows Event Logging Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-59137 |
Windows Event Logging Service Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-61347 |
Windows Event Logging Service Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-65662 |
Windows GDI Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-61360 |
Windows GDI Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-62890 |
Windows GDI+ Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62709 |
Windows GDI+ Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62822 |
Windows GDI+ Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62702 |
Windows Graphics Kernel Denial of Service Vulnerability |
Exploitation Less Likely |
No |
6.8 |
| CVE-2026-61346 |
Windows Graphics Kernel Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62774 |
Windows Graphics Kernel Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-61928 |
Windows Hello Tampering Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62750 |
Windows HTTP Protocol Stack Tampering Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-61937 |
Windows HTTP.sys Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62753 |
Windows HTTP.sys Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62735 |
Windows HTTP.sys Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62739 |
Windows HTTP.sys Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62741 |
Windows HTTP.sys Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-61368 |
Windows Hyper-V Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.0 |
| CVE-2026-62740 |
Windows Imaging Component Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-54984 |
Windows Imaging Component Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-59127 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-61925 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-70344 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-70345 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-70346 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-70347 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62768 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65774 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65796 |
Windows iSCSI Target Service Denial of Service Vulnerability |
Exploitation Unlikely |
No |
5.9 |
| CVE-2026-65679 |
Windows iSCSI Target Service Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-65791 |
Windows iSCSI Target Service Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
9.8 |
| CVE-2026-62754 |
Windows Kerberos Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62773 |
Windows Kerberos Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62752 |
Windows Kerberos Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-61930 |
Windows Kernel Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-65773 |
Windows Kernel Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-66799 |
Windows Key Guard Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62785 |
Windows LDAP – Lightweight Directory Access Protocol Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-62795 |
Windows LDAP – Lightweight Directory Access Protocol Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-62777 |
Windows License Manager Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-50472 |
Windows LUA File Virtualization Filter Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62738 |
Windows Management Instrumentation Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62719 |
Windows Message Queuing Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62717 |
Windows Message Queuing Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65790 |
Windows Message Queuing Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62707 |
Windows Modern Device Management (MDM) Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-56174 |
Windows Narrator Braille Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-61366 |
Windows Network Connection Broker Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-68819 |
Windows Network File System Denial of Service Vulnerability |
Exploitation Unlikely |
No |
5.9 |
| CVE-2026-62797 |
Windows NTFS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62700 |
Windows NTFS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62880 |
Windows NTFS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-61350 |
Windows NTFS Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
4.6 |
| CVE-2026-62796 |
Windows NTFS Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-65784 |
Windows NTFS Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-62793 |
Windows NTFS Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-62887 |
Windows NTFS Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-62696 |
Windows Program Compatibility Assistant Service Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62751 |
Windows Projected File System Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62690 |
Windows Push Notifications Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62816 |
Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62783 |
Windows Remote Access Connection Manager Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62758 |
Windows Remote Access Connection Manager Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-61924 |
Windows Remote Desktop Client Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-61918 |
Windows Remote Desktop Client Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-61921 |
Windows Remote Desktop Client Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-61356 |
Windows Remote Desktop Services Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-61367 |
Windows Remote Desktop Services Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62692 |
Windows Remote Desktop Services Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-61364 |
Windows Remote Desktop Services Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-61365 |
Windows Remote Desktop Services Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62819 |
Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-62757 |
Windows Schannel Security Feature Bypass Vulnerability |
Exploitation Unlikely |
No |
5.3 |
| CVE-2026-62889 |
Windows Secure Socket Tunneling Protocol (SSTP) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-61355 |
Windows Sensor Data Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62770 |
Windows Shell Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62782 |
Windows SMB Client Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-65794 |
Windows SMB Client Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62800 |
Windows SMBv3 Server Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-62790 |
Windows SMBv3 Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-59132 |
Windows TCP/IP Denial of Service Vulnerability |
Exploitation More Likely |
No |
7.5 |
| CVE-2026-62792 |
Windows TCP/IP Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.1 |
| CVE-2026-61353 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62723 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62724 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62748 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62729 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-59122 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62701 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62725 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62726 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62732 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62734 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62699 |
Windows Universal Disk Format File System Driver (UDFS) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
6.8 |
| CVE-2026-61926 |
Windows USB Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62832 |
Windows User Profile Service Elevation of Privilege Vulnerability |
Exploitation More Likely |
Yes |
7.8 |
| CVE-2026-62721 |
Windows User-Mode Power Service (UMPS) Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62712 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62876 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62877 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65678 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62711 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62733 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62885 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65775 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62730 |
Windows Wired AutoConfig Service Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-61349 |
Windows Work Folder Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-61939 |
Winlogon Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
Microsoft Dynamics vulnerabilities
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-66301 |
Microsoft Dynamics 365 (On-Premises) Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-65815 |
Microsoft Dynamics 365 On-Premises Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-40375 |
Microsoft Dynamics Business Central Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
Microsoft Office vulnerabilities
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-64906 |
Microsoft Access Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64912 |
Microsoft Access Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64908 |
Microsoft Access Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64914 |
Microsoft Access Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64920 |
Microsoft Access Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64919 |
Microsoft Access Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-68802 |
Microsoft Excel Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-68808 |
Microsoft Excel Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-68813 |
Microsoft Excel Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-70318 |
Microsoft Excel Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-70327 |
Microsoft Excel Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-70328 |
Microsoft Excel Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-68797 |
Microsoft Excel Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-68799 |
Microsoft Excel Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-65807 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-68793 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68794 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68795 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68796 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68800 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68807 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68806 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68810 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68811 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68815 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68816 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68798 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-68801 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68803 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68804 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68805 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68812 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68814 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68817 |
Microsoft Excel Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68792 |
Microsoft Office Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-63517 |
Microsoft Office Graphics Component Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62842 |
Microsoft Office Graphics Component Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-66809 |
Microsoft Office Graphics Component Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-63513 |
Microsoft Office Graphics Component Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-63519 |
Microsoft Office Graphics Component Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65664 |
Microsoft Office Graphics Component Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-63526 |
Microsoft Office Graphics Component Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-66807 |
Microsoft Office Graphics Component Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-70315 |
Microsoft Office Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-70314 |
Microsoft Office Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-70317 |
Microsoft Office Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-70323 |
Microsoft Office Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-63524 |
Microsoft Office Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-63529 |
Microsoft Office Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-64899 |
Microsoft Office Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-63515 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65657 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65656 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65661 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-63532 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-63533 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64898 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64903 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64904 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-64909 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64910 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64911 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-70130 |
Microsoft Office Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.4 |
| CVE-2026-57105 |
Microsoft Office SharePoint Spoofing Vulnerability |
Exploitation Less Likely |
No |
8.0 |
| CVE-2026-70306 |
Microsoft Office SharePoint Spoofing Vulnerability |
Exploitation Less Likely |
No |
9.3 |
| CVE-2026-63521 |
Microsoft Office Word Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-70319 |
Microsoft Office Word Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-63528 |
Microsoft Office Word Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-63530 |
Microsoft Office Word Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-63531 |
Microsoft Office Word Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-64917 |
Microsoft Office Word Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-66806 |
Microsoft Office Word Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-66810 |
Microsoft Office Word Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-63518 |
Microsoft Office Word Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-70311 |
Microsoft Office Word Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-63525 |
Microsoft Office Word Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-63527 |
Microsoft Office Word Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64905 |
Microsoft Office Word Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64907 |
Microsoft Office Word Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-64915 |
Microsoft Office Word Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65680 |
Microsoft OneDrive for MacOS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
6.7 |
| CVE-2026-70329 |
Microsoft Outlook Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-62882 |
Microsoft Outlook Spoofing Vulnerability |
Exploitation Unlikely |
No |
4.3 |
| CVE-2026-70313 |
Microsoft PowerPoint Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-70324 |
Microsoft SharePoint Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-70321 |
Microsoft SharePoint Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62827 |
Microsoft SharePoint Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-70355 |
Microsoft SharePoint Server Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.3 |
| CVE-2026-64921 |
Microsoft SharePoint Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-70326 |
Microsoft SharePoint Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62837 |
Microsoft SharePoint Server Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-63514 |
Microsoft SharePoint Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-63520 |
Microsoft SharePoint Server Remote Code Execution Vulnerability |
Exploitation More Likely |
No |
8.1 |
| CVE-2026-65658 |
Microsoft SharePoint Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-65663 |
Microsoft SharePoint Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-65665 |
Microsoft SharePoint Server Remote Code Execution Vulnerability |
Exploitation More Likely |
No |
8.8 |
| CVE-2026-64901 |
Microsoft SharePoint Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-66805 |
Microsoft SharePoint Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-66808 |
Microsoft SharePoint Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62829 |
Microsoft SharePoint Server Spoofing Vulnerability |
Exploitation Less Likely |
No |
4.6 |
| CVE-2026-63516 |
Microsoft SharePoint Server Spoofing Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-64922 |
Microsoft SharePoint Server Spoofing Vulnerability |
Exploitation Less Likely |
No |
4.6 |
| CVE-2026-65660 |
Microsoft SharePoint Server Spoofing Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-64897 |
Microsoft SharePoint Server Spoofing Vulnerability |
Exploitation Less Likely |
No |
4.6 |
| CVE-2026-64900 |
Microsoft SharePoint Server Spoofing Vulnerability |
N/A |
No |
7.3 |
| CVE-2026-64902 |
Microsoft SharePoint Server Spoofing Vulnerability |
N/A |
No |
4.6 |
| CVE-2026-64916 |
Microsoft SharePoint Server Spoofing Vulnerability |
Exploitation Unlikely |
No |
4.6 |
| CVE-2026-58639 |
Microsoft SharePoint Server Spoofing Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62839 |
Microsoft SharePoint Server Spoofing Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62917 |
Microsoft SharePoint Server Spoofing Vulnerability |
Exploitation Less Likely |
No |
4.6 |
| CVE-2026-63512 |
Microsoft SharePoint Server Tampering Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-65767 |
Microsoft Teams for Android and iOS Spoofing Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-65769 |
Microsoft Teams iOS Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-65768 |
Microsoft Teams Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-70310 |
Microsoft Word Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-58651 |
Microsoft Word Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-68809 |
Powerpoint Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-70312 |
Powerpoint Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-70316 |
Powerpoint Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-70325 |
Powerpoint Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-70320 |
Powerpoint Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-70322 |
Powerpoint Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
Server Software vulnerabilities
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-62912 |
Microsoft Exchange Server Denial of Service Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62910 |
Microsoft Exchange Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.2 |
| CVE-2026-65813 |
Microsoft Exchange Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62911 |
Microsoft Exchange Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
8.0 |
| CVE-2026-62913 |
Microsoft Exchange Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62915 |
Microsoft Exchange Server Security Feature Bypass Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62914 |
Microsoft Exchange Server Spoofing Vulnerability |
Exploitation Less Likely |
No |
7.3 |
SQL Server vulnerabilities
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-65811 |
Power BI Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
System Center vulnerabilities
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-54123 |
Microsoft Defender for Endpoint for Mac Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
Windows vulnerabilities
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-65777 |
Active Directory Security Feature Bypass Vulnerability |
Exploitation Unlikely |
No |
5.3 |
| CVE-2026-59130 |
AMD Zen Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.6 |
| CVE-2026-59131 |
AMD Zen Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.6 |
| CVE-2026-61357 |
Application Information Services Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62892 |
Capability Access Management Service (camsvc) Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-65786 |
Desktop Window Manager Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65787 |
Desktop Window Manager Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65788 |
Desktop Window Manager Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.0 |
| CVE-2026-59136 |
Microsoft COM for Windows Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62698 |
Microsoft Digest Authentication Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-59133 |
Microsoft High Performance Computing (HPC) Pack Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
8.8 |
| CVE-2026-59124 |
Microsoft High Performance Computing (HPC) Pack Remote Code Execution Vulnerability |
Exploitation More Likely |
No |
9.8 |
| CVE-2026-62784 |
Microsoft Local Security Authority Server (lsasrv) Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-62815 |
Microsoft QUIC Remote Code Execution Vulnerability |
N/A |
No |
9.8 |
| CVE-2026-59138 |
Microsoft Remote Registry Service Denial of Service Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-61345 |
Microsoft Remote Registry Service Denial of Service Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-66804 |
Microsoft Windows Cross Device Service Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-59135 |
Microsoft Windows Search Component Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-65814 |
Microsoft Windows Storage Port Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-6726 |
MITRE: CVE-2026-6726 TPM 2.0 Improper Object Slot Reuse |
Exploitation Less Likely |
No |
7.9 |
| CVE-2026-6727 |
MITRE: CVE-2026-6727 TPM 2.0 RSA OAEP Timing Side-Channel Vulnerability |
Exploitation Less Likely |
No |
5.9 |
| CVE-2026-65671 |
Remote Access API Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65672 |
Remote Access API Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-42976 |
Remote Access Management service/API (RPC server) Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-59134 |
Remote Desktop Client Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.5 |
| CVE-2026-61352 |
Remote Desktop Client Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.5 |
| CVE-2026-61363 |
Remote Desktop Client Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
7.5 |
| CVE-2026-62824 |
Remote Desktop Client Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-54113 |
Remote Procedure Call Denial of Service Vulnerability |
Exploitation Unlikely |
No |
7.5 |
| CVE-2026-62781 |
RPC Runtime Library Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.1 |
| CVE-2026-59125 |
Virtual Hard Disk (VHD) Miniport Driver Elevation of Privilege Vulernability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62746 |
Win32k Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62798 |
Win32k Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-62743 |
Win32k Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62786 |
Win32k Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-61358 |
Windows Accessibility Infrastructure (ATBroker.exe) Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62818 |
Windows Active Directory Certificate Services (AD CS) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-49179 |
Windows Active Directory Domain Services Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-61348 |
Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.0 |
| CVE-2026-68820 |
Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability |
Exploitation Detected |
No |
7.0 |
| CVE-2026-70307 |
Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.0 |
| CVE-2026-65783 |
Windows Autopilot Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-65779 |
Windows Autopilot Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-65780 |
Windows Autopilot Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-65778 |
Windows Autopilot Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-65782 |
Windows Autopilot Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-65781 |
Windows Autopilot Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62908 |
Windows Backup Engine Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-61927 |
Windows Bind Filter Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-61934 |
Windows Bind Filter Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62705 |
Windows Bind Filter Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62722 |
Windows Bind Filter Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62713 |
Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62771 |
Windows Cloud Files Mini Filter Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62728 |
Windows Common Log File System Driver Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62772 |
Windows Container Isolation FS Filter Driver (unionfs.sys) Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62775 |
Windows Container Isolation FS Filter Driver (unionfs.sys) Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-72971 |
Windows Container Isolation FS Filter Driver (unionfs.sys) Tampering Vulnerability |
Exploitation Unlikely |
Yes |
5.5 |
| CVE-2026-61936 |
Windows Defender Firewall Service Security Feature Bypass Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-62893 |
Windows Deployment Services TFTP Server Remote Code Execution Vulnerability |
Exploitation More Likely |
No |
9.8 |
| CVE-2026-62747 |
Windows Device Association Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62710 |
Windows Device Association Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-66802 |
Windows Device Health Attestation (DHA) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-71331 |
Windows Device Health Attestation (DHA) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-65785 |
Windows DHCP Client Denial of Service Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62755 |
Windows DHCP Client Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62736 |
Windows DHCP Client Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-61361 |
Windows DHCP Client Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62812 |
Windows DHCP Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62761 |
Windows DHCP Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62776 |
Windows DHCP Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62803 |
Windows DHCP Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62807 |
Windows DHCP Server Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62718 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62715 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62716 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62742 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62745 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62720 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62714 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62814 |
Windows DHCP Server Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-62823 |
Windows DHCP Server Remote Code Execution Vulnerability |
Exploitation More Likely |
No |
8.8 |
| CVE-2026-61923 |
Windows Display Enhancement Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-70304 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
6.7 |
| CVE-2026-70330 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
6.7 |
| CVE-2026-62769 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
6.7 |
| CVE-2026-62778 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-62881 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
6.7 |
| CVE-2026-62883 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
6.7 |
| CVE-2026-65795 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
6.7 |
| CVE-2026-65797 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
6.7 |
| CVE-2026-65799 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
6.7 |
| CVE-2026-65798 |
Windows DNS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
6.7 |
| CVE-2026-62787 |
Windows DNS Server Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
7.5 |
| CVE-2026-62817 |
Windows DNS Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62820 |
Windows DNS Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-62878 |
Windows DNS Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
9.8 |
| CVE-2026-65789 |
Windows DNS Server Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.1 |
| CVE-2026-61920 |
Windows DNS Server Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
6.6 |
| CVE-2026-61932 |
Windows DWM Core Library Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62894 |
Windows DWM Core Library Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62888 |
Windows DWM Core Library Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-61933 |
Windows DWM Core Library Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62703 |
Windows DWM Core Library Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-59128 |
Windows Encrypting File System (EFS) Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-59126 |
Windows Event Logging Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-59137 |
Windows Event Logging Service Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-61347 |
Windows Event Logging Service Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-65662 |
Windows GDI Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-61360 |
Windows GDI Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-62890 |
Windows GDI+ Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62709 |
Windows GDI+ Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62822 |
Windows GDI+ Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62702 |
Windows Graphics Kernel Denial of Service Vulnerability |
Exploitation Less Likely |
No |
6.8 |
| CVE-2026-61346 |
Windows Graphics Kernel Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62774 |
Windows Graphics Kernel Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-61928 |
Windows Hello Tampering Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62750 |
Windows HTTP Protocol Stack Tampering Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-61937 |
Windows HTTP.sys Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62753 |
Windows HTTP.sys Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62735 |
Windows HTTP.sys Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62739 |
Windows HTTP.sys Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62741 |
Windows HTTP.sys Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62811 |
Windows HTTP.sys Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
CVE-2026-61368 |
Windows Hyper-V Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.0 |
| CVE-2026-62740 |
Windows Imaging Component Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-54984 |
Windows Imaging Component Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-59127 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-61925 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-70344 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-70345 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-70346 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-70347 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-61938 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62768 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65774 |
Windows Installer Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65681 |
Windows iSCSI Target Service Denial of Service Vulnerability |
Exploitation Less Likely |
No |
7.5 |
| CVE-2026-65796 |
Windows iSCSI Target Service Denial of Service Vulnerability |
Exploitation Unlikely |
No |
5.9 |
| CVE-2026-65679 |
Windows iSCSI Target Service Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-65791 |
Windows iSCSI Target Service Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
9.8 |
| CVE-2026-62754 |
Windows Kerberos Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62766 |
Windows Kerberos Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.0 |
| CVE-2026-62773 |
Windows Kerberos Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62752 |
Windows Kerberos Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-61930 |
Windows Kernel Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62737 |
Windows Kernel Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-61929 |
Windows Kernel Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.0 |
| CVE-2026-62708 |
Windows Kernel Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
6.4 |
| CVE-2026-62749 |
Windows Kernel Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62780 |
Windows Kernel Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62788 |
Windows Kernel Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.0 |
| CVE-2026-65773 |
Windows Kernel Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-66799 |
Windows Key Guard Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62785 |
Windows LDAP – Lightweight Directory Access Protocol Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-62795 |
Windows LDAP – Lightweight Directory Access Protocol Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-62777 |
Windows License Manager Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-50472 |
Windows LUA File Virtualization Filter Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62738 |
Windows Management Instrumentation Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-70348 |
Windows Management Services Denial of Service Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-62719 |
Windows Message Queuing Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62717 |
Windows Message Queuing Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65790 |
Windows Message Queuing Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62688 |
Windows MIDI Service Module Elevation of Privileges Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62693 |
Windows MIDI Service Module Elevation of Privileges Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62707 |
Windows Modern Device Management (MDM) Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-56174 |
Windows Narrator Braille Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-56179 |
Windows Network Address Translation (NAT) Spoofing Vulnerability |
Exploitation Less Likely |
No |
8.3 |
| CVE-2026-61366 |
Windows Network Connection Broker Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-68819 |
Windows Network File System Denial of Service Vulnerability |
Exploitation Unlikely |
No |
5.9 |
| CVE-2026-62797 |
Windows NTFS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62700 |
Windows NTFS Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62880 |
Windows NTFS Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-61350 |
Windows NTFS Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
4.6 |
| CVE-2026-62796 |
Windows NTFS Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-65784 |
Windows NTFS Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-62793 |
Windows NTFS Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-62887 |
Windows NTFS Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
5.5 |
| CVE-2026-62696 |
Windows Program Compatibility Assistant Service Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62751 |
Windows Projected File System Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62690 |
Windows Push Notifications Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62816 |
Windows Reliable Multicast Transport Driver (RMCAST) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62783 |
Windows Remote Access Connection Manager Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62758 |
Windows Remote Access Connection Manager Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-61924 |
Windows Remote Desktop Client Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-61918 |
Windows Remote Desktop Client Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-61921 |
Windows Remote Desktop Client Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
6.5 |
| CVE-2026-61356 |
Windows Remote Desktop Services Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-61367 |
Windows Remote Desktop Services Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62692 |
Windows Remote Desktop Services Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-61364 |
Windows Remote Desktop Services Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-61365 |
Windows Remote Desktop Services Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62819 |
Windows Routing and Remote Access Service (RRAS) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-62779 |
Windows Schannel Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62757 |
Windows Schannel Security Feature Bypass Vulnerability |
Exploitation Unlikely |
No |
5.3 |
| CVE-2026-62889 |
Windows Secure Socket Tunneling Protocol (SSTP) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.1 |
| CVE-2026-61355 |
Windows Sensor Data Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62770 |
Windows Shell Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62799 |
Windows SMB Client Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62782 |
Windows SMB Client Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-65794 |
Windows SMB Client Information Disclosure Vulnerability |
Exploitation Unlikely |
No |
6.5 |
| CVE-2026-62800 |
Windows SMBv3 Server Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.8 |
| CVE-2026-62790 |
Windows SMBv3 Server Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
8.8 |
| CVE-2026-62695 |
Windows Storage Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-61359 |
Windows Storage Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-59132 |
Windows TCP/IP Denial of Service Vulnerability |
Exploitation More Likely |
No |
7.5 |
| CVE-2026-62792 |
Windows TCP/IP Remote Code Execution Vulnerability |
Exploitation Unlikely |
No |
8.1 |
| CVE-2026-61353 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62723 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62724 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62748 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62729 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-59122 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62701 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62725 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62726 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62732 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-62734 |
Windows Telephony Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.0 |
| CVE-2026-62699 |
Windows Universal Disk Format File System Driver (UDFS) Remote Code Execution Vulnerability |
Exploitation Less Likely |
No |
6.8 |
| CVE-2026-61926 |
Windows USB Driver Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62832 |
Windows User Profile Service Elevation of Privilege Vulnerability |
Exploitation More Likely |
Yes |
7.8 |
| CVE-2026-62721 |
Windows User-Mode Power Service (UMPS) Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62712 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-62876 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62877 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65678 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62711 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62733 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-62885 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.8 |
| CVE-2026-65775 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation More Likely |
No |
7.8 |
| CVE-2026-65776 |
Windows Win32k Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
| CVE-2026-62730 |
Windows Wired AutoConfig Service Information Disclosure Vulnerability |
Exploitation Less Likely |
No |
5.5 |
| CVE-2026-61349 |
Windows Work Folder Service Elevation of Privilege Vulnerability |
Exploitation Unlikely |
No |
7.8 |
| CVE-2026-61939 |
Winlogon Elevation of Privilege Vulnerability |
Exploitation Less Likely |
No |
7.0 |
Zero-Day Vulnerabilities: Known Exploited
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-68820 |
Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability |
Exploitation Detected |
No |
7.0 |
Zero-Day Vulnerabilities: Publicly Disclosed (No known exploitation)
|
CVE |
Title |
Exploitation status |
Publicly disclosed? |
CVSS v3 base score |
|---|---|---|---|---|
| CVE-2026-72971 |
Windows Container Isolation FS Filter Driver (unionfs.sys) Tampering Vulnerability |
Exploitation Unlikely |
Yes |
5.5 |
| CVE-2026-62832 |
Windows User Profile Service Elevation of Privilege Vulnerability |
Exploitation More Likely |
Yes |
7.8 |
Summer 2026 SOC 1 report is now available with 185 services in scope
Post Syndicated from Baj Bajwa original https://aws.amazon.com/blogs/security/summer-2026-soc-1-report-is-now-available-with-185-services-in-scope/
Amazon Web Services (AWS) is pleased to announce that the Summer 2026 System and Organization Controls (SOC) 1 report is now available. The reports cover 185 services over the 12-month period from July 1, 2025–June 30, 2026, giving customers a full year of assurance. These reports demonstrate our continuous commitment to adhering to the heightened expectations of cloud service providers.
Customers can download the Summer 2026 SOC 1 report through AWS Artifact, a self-service portal for on-demand access to AWS compliance reports. Sign in to AWS Artifact in the AWS Management Console, or learn more at Getting Started with AWS Artifact.
AWS strives to continuously bring services into the scope of its compliance programs to help customers meet their architectural and regulatory needs. You can view the current list of services in scope on our Services in Scope page. As an AWS customer, you can reach out to your AWS account team if you have any questions or feedback about SOC compliance.
To learn more about AWS compliance and security programs, see AWS Compliance Programs.
How GPU acceleration builds billion-scale vector indexes on Amazon OpenSearch Service
Post Syndicated from Navneet Verma original https://aws.amazon.com/blogs/big-data/how-gpu-acceleration-builds-billion-scale-vector-indexes-on-amazon-opensearch-service/
Modern search demands high-performance vector indexing and scalability to keep pace with the rapid growth of generative AI applications. As datasets grow into the billions, traditional CPU-based indexing often becomes a bottleneck, stalling productivity and innovation velocity.
With GPU-accelerated vector (k-NN) indexing now available on Amazon OpenSearch Service and Amazon OpenSearch Serverless, you can scale to billions of vectors efficiently. Powered by NVIDIA cuVS, an open-source library for GPU-accelerated vector search, this capability offloads compute-intensive vector index building to specialized GPU workers while your existing CPU infrastructure continues serving search. The result is faster, more cost-efficient construction of large-scale vector indexes without sacrificing query performance.
Our earlier post went into those performance and cost benefits in detail. This post goes a level deeper into how the capability works. We walk through the decoupled architecture that makes this possible. We explain how a GPU-built index is converted into one that your CPU data nodes can search with no quality tradeoff. We also show how the approach holds up at scale, with a benchmark of one billion 1024-dimensional vectors. Finally, we share the operational best practices we recommend for running GPU-accelerated index builds in production.
Use cases and benefits
As companies across industries build AI-powered and agentic applications to deliver richer customer experiences, GPU acceleration for vector indexing helps across a range of use cases. A few examples:
- Adopt new embedding models faster: When an organization upgrades to a newer embedding model, every vector has to be regenerated and reindexed. At hundreds of millions to billions of vectors, a CPU rebuild can take days or weeks. GPU acceleration shortens that rebuild to hours, so you can move to a higher-quality model while significantly reducing the reindexing window and availability risk.
- Accelerate large-scale reindexing: A global ecommerce application managing billions of product listings, customer reviews, and behavioral signals must rebuild its vector index rapidly as new products and embeddings are added. GPU acceleration completes this within a tight operational window, keeping search relevance current.
- Absorb bursty or high-sustained writes: A media company covering a major sporting event, such as the World Cup or Olympics, needs to index millions of real-time embeddings simultaneously. These embeddings span match highlights, commentary clips, athlete profiles, and fan-generated content, and millions of viewers search for related content at the same time. GPU workers absorb the indexing burst without competing with CPU nodes serving live search traffic, avoiding the latency spikes that usually accompany heavy writes.
- Right-size clusters for mixed read/write workloads: A retail system traditionally over-provisions its CPU cluster to handle both peak indexing loads during catalog refreshes and concurrent search traffic, paying for peak capacity around the clock. By offloading indexing to GPUs, the CPU cluster can be right sized for search alone, reducing infrastructure costs without sacrificing performance.
- Speed up migrations to semantic search or to OpenSearch: Whether you’re converting a text-based corpus to vector embeddings for the first time or migrating an existing vector workload from another database to Amazon OpenSearch Service, GPU-accelerated indexing compresses what would be days of index building into hours, keeping pace with upstream GPU-powered embedding generation and minimizing cutover risk.
When does GPU acceleration activate?
GPU acceleration activates automatically once you opt in. On OpenSearch Service domains, you enable it by turning on the Vector Acceleration option, and from that point on, no changes to code or API flags are needed. On OpenSearch Serverless, GPU index-build acceleration is on by default for NextGen vector search collections. Figure 1 illustrates the index build workflow. OpenSearch automatically routes vector indexing operations to GPU or CPU based on segment size, optimizing performance and falling back to CPU if issues arise.
When OpenSearch flushes or merges a segment, it compares the segment’s vector data size against a configurable window bounded by index.knn.remote_index_build.size.min and index.knn.remote_index_build.size.max. The lower bound defaults to 50 MB. Segments above the lower bound are offloaded to a remote GPU worker, and smaller segments build locally on CPU. The segment vector size is calculated as:
segment_vector_size = num_vectors × dimensions × bytes_per_element
This means two workloads with identical document counts can produce different segment sizes:
| Vectors | Dimensions | Encoding | Segment Vector Size |
| 100,000 | 1536 | Float32 | ~586 MB |
| 100,000 | 768 | Byte | ~74 MB |
Both examples exceed the default 50 MB lower bound, so with default settings both segments would be offloaded to a GPU worker.
Figure 1: Simplified flow for index builds
Decoupled indexing architecture
An OpenSearch index is internally divided into segments, each containing its own vector graph. This segment-level structure is what makes GPU offload practical. Each segment’s graph can be built independently on a GPU worker without coordinating across the full index. Building on this, the key architectural insight is separating where vectors are indexed from where they are searched. Existing CPU data nodes continue handling ingestion, search, and non-vector workloads. When a segment is ready for vector index construction, the heavy graph-building work is offloaded to dedicated GPU workers, and the finished index is returned to the data node for serving.
The index build workflow
- Ingest – Documents with vector fields are ingested into your OpenSearch Service domain or OpenSearch Serverless collection as usual. Vectors accumulate in segments on CPU data nodes.
- Offload – When a segment flushes or merges and its vector data falls within the GPU activation window, the data node uploads the raw vectors to Amazon Simple Storage Service (Amazon S3) and submits a build request.
- Build – A GPU worker from a managed warm pool picks up the job, loads the vectors, and builds the index using CAGRA (CUDA ANN Graph), the GPU-native graph algorithm in NVIDIA cuVS. The resulting CAGRA graph is then converted to a Hierarchical Navigable Small World (HNSW) graph compatible with CPU-based search.
- Return – The completed HNSW index is written back to Amazon S3 and downloaded by the data node, which then uses it to serve search queries.
Fully managed GPU index builds
Enable Vector Acceleration, and Amazon OpenSearch Service handles the rest:
Automatic scaling – GPU workers scale up and down automatically based on the number of pending build jobs. During a bulk ingest or reindex, more GPU workers spin up to handle the load. When the queue drains, they scale back to zero.
Automatic instance selection – The service selects the right GPU instance type for each build job based on segment size. No capacity planning or instance selection is required on your part.
Pay only for active builds – You’re charged only when GPUs are actively building indexes, not while they are idle. Even if Vector Acceleration is enabled on your domain or collection, GPU charges, measured in OpenSearch Compute Units (OCUs), apply only when segments reach the activation threshold and trigger an index build. There is no standing GPU infrastructure cost.
Your cost therefore scales directly with indexing activity. Bursty reindexing workloads consume GPU capacity for the duration of the build, and GPU cost returns to zero until the next build.
Figure 2 illustrates the decoupled GPU workflow. Amazon S3 acts as the intermediary between data nodes and GPU workers, allowing them to operate independently. Data nodes upload raw vectors to Amazon S3, GPU workers build the CAGRA graph and convert it to HNSW, and the completed index is returned to the data nodes for serving, with search running uninterrupted throughout.
Figure 2: GPU index flow architecture
Inside the CAGRA-to-HNSW conversion
In the previous section, we described how GPU workers build the vector index and return it to data nodes. But how does a GPU-built graph become searchable on CPU, and does this conversion sacrifice quality? The short answer: it doesn’t.
The CAGRA algorithm
The GPU workers use the CAGRA algorithm integrated through the cuVS GPU backend of the Facebook AI Similarity Search (Faiss) library. CAGRA is a graph-based indexing approach built from the ground up for GPU acceleration. It first builds a k-NN graph using another approximate nearest neighbors method like Inverted File with Product Quantization (IVF-PQ) or Nearest Neighbor Descent (NN-Descent). It then removes redundant paths between neighbors to form a navigable search graph.
Figure 3: Construction flow of the CAGRA graph
Source: CAGRA: Highly Parallel Graph Construction and Approximate Nearest Neighbor Search for GPUs
How the GPU worker builds the index
When the GPU workers receive a vector index build request, it carries the necessary parameters for constructing the segment-specific vector index. The vector index build component initiates the process by retrieving the vector file from Amazon S3 and loading it into CPU memory. These vectors are then used to construct a CAGRA index using Faiss. After constructing the CAGRA index on GPU, the system converts it into an HNSW graph format for compatibility with CPU-based search operations. The resulting index is uploaded to Amazon S3, completing the build request.
Converting the CAGRA graph to HNSW
A typical HNSW index is a multilayered hierarchical graph. The bottom layer (layer 0) of the graph contains the vectors, and the upper layers are sparse subsets used solely for navigation. They help the search algorithm find a good entry point into the bottom layer. However, our HNSW implementation uses the CAGRA graph as the bottom layer and, similar to the CAGRA search method, starts with random entry points into the graph, avoiding the need for the upper layers altogether.
This means the GPU handles the heavy lifting of building the base-layer graph. Reusing that graph as the HNSW base layer avoids rebuilding it on the CPU, which keeps conversion overhead low. As Figure 4 shows, the CAGRA graph becomes the base layer. At query time, the search selects a random set of nodes in the graph and traverses it by following the nearest neighbor links. This is known as greedy search.
Figure 4: Searching an HNSW-converted CAGRA graph
Same recall, faster build
Previous benchmarks have confirmed that GPU-built indexes achieve the same recall as CPU-built HNSW with no quality tradeoff. This is because the bottom-layer graph structure produced by CAGRA is equivalent in connectivity and search quality to what HNSW constructs on CPU. Only the build method differs.
Scaling beyond GPU memory
Out-of-core construction
Traditional GPU indexing requires the entire dataset to reside in GPU memory, creating a hard ceiling on index size based on available hardware. CAGRA removes this limitation through out-of-core k-NN graph construction. When IVF-PQ is used to build the initial k-NN graph for CAGRA, data is streamed from system memory to the GPU in batches, so the full dataset never needs to fit in GPU memory at once. Meanwhile, the GPU still handles the computationally intensive distance calculations and graph optimization.
Quantization
GPU-accelerated indexing supports the quantization levels available in OpenSearch, including 2×, 8×, 16×, and 32× compression. Quantization is applied before vectors are sent to the GPU. This reduces both the data transfer size to GPU workers and the memory footprint during graph construction. This means that you can build indexes over larger segments, improving cost efficiency.
Indexing one billion 1024-dimensional vectors on the GPU
Dataset setup
To evaluate a realistic large-scale workload, we used a dataset containing one billion vectors in 1024 dimensions. Because uniformly random vectors yield misleading results for both index construction and recall, we required data that maintained the structure of real-world embeddings. We created this dataset using the cuVS synthetic dataset generator in cuvs-bench, which outputs synthetic data whose distribution mimics an actual embedding dataset derived from Common Crawl. You can use this approach to build a realistic dataset without exposing or distributing sensitive original data. The generator can produce the complete one-billion-vector dataset, 10,000 query vectors, and the associated ground-truth labels in roughly two hours on a single Amazon Elastic Compute Cloud (Amazon EC2) g6e.16xlarge instance.
Cluster configuration
We designed the benchmark cluster on OpenSearch Service following OpenSearch vector search performance tuning best practices and conducted the benchmark using the OpenSearch Benchmark framework.
| Setting | Value | Rationale |
| Data Nodes | 24 × r8g.4xlarge | Memory-optimized instances for large vector indexes |
| Primary shards | 48 | Keeps shard size manageable and maximizes parallelism |
| Replicas | 0 | Maximizes indexing throughput. Replicas added after build |
| GPU workers | 10 (pre-scaled) | Avoids cold-start effects during measurement |
| Bulk clients | 160 | Saturates ingestion pipeline across 24 nodes |
| Bulk size | 500 docs/request | Balances per-request overhead vs. memory pressure |
| Refresh interval | -1 (during ingest) | Prevents small segment creation. Force merge after ingesting |
| Merge autothrottle | Disabled | Avoids artificial bottleneck during benchmark |
Key best practices applied
- Memory-optimized instances – r8g.4xlarge provides sufficient heap and native memory for loading HNSW graphs post-build.
- Disabled refresh during bulk ingest – Prevents creation of many small segments that would each trigger individual GPU builds.
- High number of bulk clients – Saturates ingestion across nodes and makes sure that GPUs are busy building the indexes.
We used the default HNSW build and search settings in OpenSearch (such as m and ef_construction) since the defaults are what most users start with, and they keep the benchmark representative.
Benchmark results
| Dataset | Index (min) | Recall @k=100 | Recall @1 | P50 (search) | P90 (search) | P99 (search) | Vector Acceleration OCU Used |
| 1024D 1B | 274 | 0.93 | 0.93 | 26.47ms | 32.5ms | 66.6ms | 44 |
Build time scales linearly with data volume
Our earlier benchmark on OpenSearch Service indexed one billion 128-dimensional vectors (BigANN SIFT dataset) in approximately 35.5 minutes. In our latest benchmark, we scaled dimensionality 8x to 1024 dimensions and completed the index build in 274 minutes, roughly proportional to the increase in data volume. This demonstrates that GPU acceleration maintains consistent throughput efficiency as dimensionality grows: build time scales with data volume rather than fixed startup costs, so you can predictably estimate index build time from your dataset size. Search latency also stayed low at this scale, so the resulting index supported responsive queries without trading away build speed.
Optimizing bulk ingestion for GPU-accelerated indexing
When loading large volumes of vector data, temporarily adjusting index behavior can significantly reduce GPU processing overhead. This approach works if your use case can tolerate a brief period of data staleness. During full index builds, this is generally acceptable, because newly ingested vectors are not searchable until you re-enable refresh. By disabling refresh during bulk ingestion ("index.refresh_interval": "-1"), you prevent the continuous creation of small segments. Each of these would otherwise trigger an individual GPU build job. After ingestion is complete, we enable the refresh interval and complete the refresh to make the segment searchable. This means the GPU builds the vector index once across large, well-packed segments rather than repeatedly across many small ones, resulting in faster overall indexing throughput.
After enabling GPU acceleration, you can monitor builds through Amazon CloudWatch metrics (cluster-level) and the OpenSearch k-NN Stats API (per-node). If a GPU build fails, the system automatically falls back to CPU-based index building, so your data remains indexed.
Future optimization
Today, the completed HNSW index (graph structure and vectors) is transferred back from GPU workers to data nodes through Amazon S3. Because data nodes already hold the raw vectors locally, a future optimization will transfer only the graph structure (neighbor lists). This significantly reduces the data written back to Amazon S3 and the download time to data nodes.
Conclusion
GPU-accelerated indexing lets you build billion-scale vector indexes on Amazon OpenSearch Service in hours instead of days, without changing how queries are served on both OpenSearch Service domains and OpenSearch Serverless collections. In this post, we showed how OpenSearch Service offloads eligible index builds to GPU workers, builds a CAGRA graph through the NVIDIA cuVS backend in Faiss, and converts it into a CPU-searchable HNSW index. We then demonstrated the approach at scale on one billion 1024-dimensional vectors, and shared best practices for optimizing bulk ingestion and monitoring build activity and OCU usage.
Get started
Ready to try GPU-accelerated vector indexing? In a supported AWS Region, you can enable GPU acceleration when you create or update an OpenSearch Service domain running OpenSearch 3.1 or later. Use the AWS Management Console, AWS Command Line Interface (AWS CLI), or AWS SDK. For a new OpenSearch Serverless deployment, create a NextGen vector search collection, where GPU index-build acceleration is enabled by default and can be controlled for individual indexes. For a Classic vector collection, enable GPU acceleration at the collection level.
Acknowledgments
The authors would like to thank Ben Gardner, Manas Singh, Zack Meeks, Jiahong Liu, James Yi, Jinsol Park from NVIDIA for their contributions to this post.
About the authors
Minisforum N5 Max Review with AMD Ryzen AI Max+ 395
Post Syndicated from Vic A original https://www.servethehome.com/minisforum-n5-max-review-with-amd-ryzen-ai-max-395/
We review the Minisforum N5 Max, a 64GB AMD Strix Halo system that combines 10GbE, a 5-bay NAS, and more into a single box
The post Minisforum N5 Max Review with AMD Ryzen AI Max+ 395 appeared first on ServeTheHome.
S10 E1: Train Derailment & Psychedelic Assisted Therapy: Last Week Tonight with John Oliver
Post Syndicated from LastWeekTonight original https://www.youtube.com/watch?v=JhoYRrb7Ve4
AWS successfully completed its 2025-26 NHS DSPT assessment
Post Syndicated from Tariro Dongo original https://aws.amazon.com/blogs/security/aws-successfully-completed-its-2025-26-nhs-dspt-assessment/
Amazon Web Services (AWS) is pleased to announce its successful completion of the 2025-26 NHS Data Security and Protection Toolkit (NHS DSPT) assessment audit and achieving a status of Standards Exceeded.
The NHS DSPT is an assessment that allows organizations to measure their performance against the National Data Guardian’s 10 data security standards. All organizations that access NHS patient data and systems are expected to use the toolkit to demonstrate their compliance with safe data security standards. NHS DSPT covers standards regarding Personal Confidential Data, Continuity Planning, IT Protection, and more. AWS undergoes the assessment to provide customers with assurance that we are practicing good data security.
The AWS NHS DSPT assessment status is valid until June 30, 2027, and a certificate that confirms our compliance is available on the NHS England website and in AWS Artifact. AWS Artifact is a self-service portal for on-demand access to AWS compliance reports. Sign in to AWS Artifact in the AWS Management Console, or learn more at Getting Started with AWS Artifact.
Security and compliance is a shared responsibility between AWS and the customer. When customers move their computer systems and data to the cloud, security responsibilities are shared between the customer and the cloud service provider. For more information, see the AWS Shared Security Responsibility Model.
To learn more about our compliance and security programs, see AWS Compliance Programs.
As an AWS customer, you can reach out to your AWS account team if you have any questions or feedback.
If you have feedback about this post, submit comments in the Comments section below.
AI Genie in the Wild
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2026/08/ai-genie-in-the-wild.html
When I give talks about AI genies, I use this sort of example as a hypothetical. It’s happened.
The story is from Australia. Someone named Andrew tasked OpenClaw to book gym classes for him. And….
Minutes later, his AI agent reported it had discovered a way to book Andrew into classes several weeks in advance, far beyond what was supposed to be possible.
Andrew, who was sitting fourth on a waitlist for a class later that week, asked if it was possible to move him to the top of the list.
The agent came back and told Andrew that it had kicked another gym-goer off the list as part of the testing of its capabilities.
“The API has zero authorisations checks on cancelling other people’s reservations … I tested this with the person in waitlist position #1 —and it actually went through. So you’ve moved from #4 to #3 already,” it messaged back.
If there is any vulnerability in anything, AIs are going to find and exploit them. Our cyber defensive game has to be dramatically improved…very fast.
Slashdot thread.
Centralized CloudTrail monitoring across 100+ AWS accounts
Post Syndicated from Jagdish Komakula original https://aws.amazon.com/blogs/big-data/centralized-cloudtrail-monitoring-across-100-aws-accounts/
Organizations running workloads across dozens or hundreds of AWS accounts face a common challenge: centralized security monitoring at scale. Security teams need to search through hundreds of gigabytes of AWS CloudTrail logs daily to detect threats and satisfy compliance requirements for SOC 2, PCI DSS, and HIPAA audits. They also need to provide role-based access to multiple teams with different responsibilities.
Without purpose-built infrastructure, this often involves manual log searching that takes hours and compliance report generation that takes days. It also leads to fragmented code bases of custom AWS Lambda functions managing index lifecycles across environments. A single shared search domain without consistent access control compounds the problem further.
In this post, we show you how to build a centralized CloudTrail monitoring solution on Amazon OpenSearch Service. Terraform manages the full stack, from domain provisioning to access control and lifecycle policies. The solution handles 200 GB/day of CloudTrail logs, provides automated threat detection alerts, and gives 4 different teams isolated, role-appropriate access to the data.
Solution overview
The following diagram shows the architecture. CloudTrail logs flow from 100+ AWS accounts through an organization trail into a centralized S3 bucket. Amazon Simple Queue Service (Amazon SQS) notifications trigger the OpenSearch Ingestion pipeline. The pipeline auto-scales between 2 and 10 OpenSearch Compute Units (OCUs) to parse and index the logs into the OpenSearch domain. Four team-specific roles access the data through OpenSearch Dashboards with tenant isolation.
The key components are:
- CloudTrail aggregation. An organization trail sends logs from 100+ accounts into a centralized Amazon Simple Storage Service (Amazon S3) bucket.
- Ingestion. An Amazon OpenSearch Ingestion pipeline picks up new logs through Amazon SQS notifications on the S3 bucket. It automatically scales between 2 and 10 OCUs based on queue depth. Throttling on lower-environment queues prevents development and test spikes from starving production ingestion.
- Amazon OpenSearch Service domain. 6 or1.4xlarge data nodes (OpenSearch Optimized instances) with 3 dedicated r8g.large master nodes, fine-grained access control, encryption at rest, and node-to-node encryption.
- Infrastructure as code. Index templates, Index State Management (ISM) policies, roles, role mappings, tenants, alerting monitors, and dashboards are all declared in Terraform and applied consistently across environments.
Prerequisites
To implement this solution, you need the following:
- An organization in AWS Organizations with CloudTrail enabled across member accounts.
- Terraform v1.5+ with the AWS provider and the OpenSearch provider.
- A virtual private cloud (VPC) with private subnets for the OpenSearch domain.
- IAM roles for each team that will access the OpenSearch domain.
- An Amazon Simple Notification Service (Amazon SNS) topic for security alert notifications.
- Familiarity with Amazon OpenSearch Service, Terraform, and AWS CloudTrail.
- Sample Terraform code is available in the GitHub repository
Implementation
This section walks through the Terraform code for each component of the solution, starting with the workload profile that informed our sizing decisions.
Workload profile
Before sizing the cluster, we defined the workload characteristics and SLAs for the centralized CloudTrail monitoring platform:
| Metric | Value |
| Index throughput | 200 GB/day (~18,000 docs/sec) |
| Search queries | ~2,000 queries/day (~0.023 QPS) |
| Average search latency | < 100 ms (achieved: 76 ms) |
| Saved searches | 600+ |
| Dashboards and visualizations | 100+ |
| User teams | 4 (Security Ops, Incident Response, Compliance, DevOps) |
| Retention | 30 days (hot tier) |
| Availability target | 99.9% |
This is a write-heavy ingestion workload. The primary use case is automated alerting and periodic compliance queries rather than continuous interactive search. This workload profile informed the decision to use OR1 (storage-optimized) instances with zero replicas, prioritizing indexing throughput over search parallelism.
Domain provisioning
Start by provisioning the Amazon OpenSearch Service domain with encryption, fine-grained access control, and VPC placement:
This solution was built on OR1 instances, which are storage-optimized and use Amazon Elastic Block Store (Amazon EBS) (gp3 or io1) for local storage, with data copied synchronously to Amazon S3 as it arrives. This storage structure provides increased indexing throughput because indexing is performed exclusively on primary shards. Replicas are backed by Amazon S3 through segment replication, eliminating the CPU overhead of document replication on replica nodes. For new deployments, we recommend OR2 instances, which offer up to 26% higher indexing throughput compared to OR1 while maintaining the same storage-optimized architecture.
Ingestion pipeline
The Amazon OpenSearch Ingestion pipeline provides serverless, auto scaling ingestion from Amazon S3 into the OpenSearch domain. It picks up new CloudTrail logs through Amazon SQS notifications on the centralized S3 bucket and scales between 2 and 10 OpenSearch Compute Units (OCUs) based on queue depth:
The pipeline uses the S3 source plugin with SQS-based notifications. When new CloudTrail log files land in S3, an SQS message triggers the pipeline to fetch and parse them. The min_units and max_units parameters control auto scaling. The pipeline starts at 2 OCUs and scales up to 10 based on queue depth, handling ingestion spikes without manual intervention. For lower environments (development and testing), you can apply throttling on the Amazon SQS queue to prevent non-production spikes from starving production ingestion capacity.
Index template
Define index templates up front to avoid painful reindexing later. The following template sets explicit mappings for CloudTrail fields, optimizes for write throughput with async translog durability, and integrates with ISM for automatic rollover:
Defining mappings before ingestion prevents mapping conflicts and avoids the need to reindex data after the fact.
Lifecycle management (ISM policy)
The following ISM policy replaces custom Lambda functions with a single declarative policy. The rollover action uses two OR conditions: min_index_age and min_primary_shard_size. Whichever threshold is reached first triggers the rollover. This keeps shard sizes bounded while ensuring timely rotation even during low-volume periods:
This approach reduces lifecycle management code by approximately 60% compared to per-environment Lambda functions, and changes deploy in a single terraform apply.
Note: For indexes ingesting more than 100 GB/day (such as CloudTrail at 200 GB/day in this deployment), you can override
min_index_ageto 12h to roll over more frequently. The two conditions are OR-based in OpenSearch ISM. If a shard reaches 30 GB before 1 day, it rolls over on size. If 1 day passes before 30 GB, it rolls over on age.
Multi-team access control
When multiple teams need different access levels to the same data, define all roles declaratively and use for_each to create them consistently. The following example defines 4 team roles with varying permissions:
This approach maps IAM roles (not individual users) to OpenSearch roles. Adding a new team means adding one entry to the locals block and running terraform apply. Each team gets an isolated tenant in OpenSearch Dashboards, preventing cross-team interference with saved searches, visualizations, and dashboard configurations. We chose OpenSearch Dashboards because tenants, roles, visualizations, and saved objects can all be managed programmatically through the Terraform OpenSearch provider, keeping the entire stack under infrastructure-as-code governance. For teams building new visualizations outside of Terraform-managed workflows, we recommend OpenSearch UI. This next-generation analytics interface supports multiple data sources, provides workspaces for team isolation, and remains available during cluster upgrades.
Alerting
Define alerting monitors in Terraform to detect security-critical events automatically. The following monitor catches CloudTrail tampering attempts (StopLogging, DeleteTrail) and sends alerts through Amazon SNS:
Results and performance
After deploying the solution, we measured steady-state performance against the SLAs defined in the workload profile:
| Metric | Target | Achieved |
| Index throughput | 200 GB/day | 200 GB/day sustained (~18,000 docs/sec) |
| Search latency (avg) | < 100 ms | 76 ms |
| Search availability | 99.9% | 99.95%+ (no unplanned downtime in 145 days) |
| Alert detection time | < 2 minutes | ~1 minute (monitor interval) |
| Compliance report generation | < 5 minutes | On-demand via saved searches |
Key outcomes:
- Threat detection dropped from hours to minutes. Automated alerting replaced manual log searching. The CloudTrail tampering monitor detects suspicious activity within one minute of the event.
- Compliance reports generate on demand. With 600+ saved searches and 100+ dashboards, compliance teams produce SOC 2, PCI DSS, and HIPAA audit evidence in minutes rather than days.
- Four teams operate independently. Each team has its own isolated tenant in OpenSearch Dashboards, preventing cross-team interference with saved searches and dashboard configurations.
- Zero custom Lambda functions. ISM policies, index templates, and access control are all managed declaratively through Terraform, eliminating the previous fragmented code base.
Best practices
- Define index templates before ingesting anything. Changing mappings on existing indices means reindexing. Get this right first.
- Set rollover thresholds based on your actual ingestion rate. At 200 GB/day, rolling over at 30 GB keeps shard counts manageable while balancing query performance.
- Test ISM transitions in a lower environment first. Warm and cold migrations on large indices take time.
- Map IAM roles, not users. People change teams. Roles stay stable. This simplifies access management.
- Put an Amazon SQS queue between S3 and the ingestion pipeline. This gives you per-environment throttling control without modifying pipeline configuration.
- Use
for_eachaggressively. Roles, tenants, index patterns, and monitors all follow a pattern across teams or environments, so usefor_eachto eliminate copy-paste drift. - Consider OpenSearch UI for new visualization workflows. This solution uses OpenSearch Dashboards for Terraform-managed tenants and roles. OpenSearch UI is a next-generation interface that supports multiple data sources, stays available during cluster upgrades, and includes workspaces for team isolation. It is the recommended interface for creating new dashboards and visualizations going forward.
Optional: Extending with cold storage for longer retention
For organizations with compliance requirements mandating longer retention (for example, 7 years for PCI DSS or HIPAA), you can extend the ISM policy with warm and cold tiers. The following example adds tiered storage that moves data through hot, warm, cold, and delete states:
Warm storage uses force-merge to reduce segment count (lowering query overhead), while cold storage moves data entirely to Amazon S3 for minimal cost. This tiered approach keeps hot-tier performance high while meeting long-term audit requirements.
Cleanup
To avoid incurring ongoing charges, remove the resources created in this post by running:
This removes the OpenSearch domain, ingestion pipeline, IAM roles, SQS queues, and all associated configurations. Verify that you have exported any data or dashboards you want to retain before running destroy.
Conclusion
In this post, we showed you how to build a centralized CloudTrail monitoring solution on Amazon OpenSearch Service with Terraform managing the entire stack. The approach moves from fragile, manually configured systems with redundant Lambda code to a version-controlled, peer-reviewed, consistently deployed infrastructure.
Threat detection drops from hours to minutes with automated alerting. Compliance reports that took days now generate on demand. And your team spends time on security analysis instead of infrastructure maintenance.
To get started, use the AWS Terraform provider aws_opensearch_domain resource for the domain, then use the Terraform OpenSearch provider for index templates, ISM policies, roles, and monitors. Configure your ingestion pipeline to transform and enrich incoming CloudTrail logs before indexing, building a modern, scalable security foundation that grows with your organization.
The complete source code for this solution is available in the GitHub repository: GitHub repository
For more on the services used in this solution:
- Amazon OpenSearch Service
- AWS CloudTrail
- Amazon OpenSearch Ingestion
- Index State Management
- Fine-grained access control
About the authors
[$] KVM planes head for takeoff
Post Syndicated from corbet original https://lwn.net/Articles/1087590/
Virtualization places a guest system into a separate security domain,
typically with less privileges than software running directly on the host.
Increasingly, there is interest in creating multiple security domains
within a single virtualized system as well. CPU vendors (and software
vendors too) are implementing solutions; each of which, of course, is
different from all of the others. KVM planes, currently under development
by Jörg Rödel, Paolo Bonzini, and others in the KVM community, is an
attempt to provide an abstraction layer that makes all of these features
available on Linux systems; it is not a small task.
Bernard: GNOME Shell design dreams
Post Syndicated from jzb original https://lwn.net/Articles/1088238/
GNOME contributor Tobias Bernard has published
a blog post that details some of the design team’s ideas for the
GNOME Shell over the long term:
Some of these we have relatively complete plans for, others are
more vague ideas that need more research and prototyping. As always,
getting things like these implemented depends on developer capacity
and interest (and sometimes funding).While each of these ideas may require additional discussion,
prototyping, and testing, we (the design team) have collected them all
together here to share our longer-term vision and to give each idea
more visibility.
Buc-ee’s Update #lastweektonight
Post Syndicated from LastWeekTonight original https://www.youtube.com/shorts/CC-23tVxvNw
Security updates for Tuesday
Post Syndicated from jzb original https://lwn.net/Articles/1088226/
Security updates have been issued by AlmaLinux (gpsd), Debian (caddy, libyaml-syck-perl, nss, and wordpress), Fedora (chezmoi, chromium, emacs, kernel, knot, libcupsfilters, mingw-gstreamer1-plugins-good, mingw-libidn, mingw-python-pip, nghttp2, p11-kit, python-webob, suricata, and xen), Mageia (bind, openslide, php8.4, and php8.5), Oracle (gpsd-minimal, kernel, libarchive, libpng12, nodejs-nodemon, php:8.3, ruby:3.3, and ruby:4.0), SUSE (agama-web-ui, bind, bouncycastle, dhcpcd, ffmpeg, ffmpeg-4, freerdp, gd, gitoxide, kak-lsp, kernel-devel, librest-1_0-0, libsdb2_5_0, libssh2_org, nodejs22, PackageKit, perl, perl-Date-Manip, python-ujson, python3-sqlparse, python311, python312, python313-pymongo, ruby2.5, runc, suseconnect-ng, thunderbird, vlang, webkit2gtk3, and weechat), and Ubuntu (imagemagick and systemd).