Tag Archives: Uncategorized

SQL Injection Attack on Airport Security

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/09/sql-injection-attack-on-airport-security.html

Interesting vulnerability:

…a special lane at airport security called Known Crewmember (KCM). KCM is a TSA program that allows pilots and flight attendants to bypass security screening, even when flying on domestic personal trips.

The KCM process is fairly simple: the employee uses the dedicated lane and presents their KCM barcode or provides the TSA agent their employee number and airline. Various forms of ID need to be presented while the TSA agent’s laptop verifies the employment status with the airline. If successful, the employee can access the sterile area without any screening at all.

A similar system also exists for cockpit access, called the Cockpit Access Security System (CASS). Most aircraft have at least one jumpseat inside the cockpit sitting behind the flying pilots. When pilots need to commute or travel, it is not always possible for them to occupy a revenue seat, so a jumpseat can be used instead. CASS allows the gate agent of a flight to verify that the jumpseater is an authorized pilot. The gate agent can then inform the crew of the flight that the jumpseater was authenticated by CASS.

[attack details omitted]

At this point, we realized we had discovered a very serious problem. Anyone with basic knowledge of SQL injection could login to this site and add anyone they wanted to KCM and CASS, allowing themselves to both skip security screening and then access the cockpits of commercial airliners.

We ended up finding several more serious issues but began the disclosure process immediately after finding the first issue.

Adm. Grace Hopper’s 1982 NSA Lecture Has Been Published

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/08/adm-grace-hoppers-1982-nsa-lecture-has-been-published.html

The “long lost lecture” by Adm. Grace Hopper has been published by the NSA. (Note that there are two parts.)

It’s a wonderful talk: funny, engaging, wise, prescient. Remember that talk was given in 1982, less than a year before the ARPANET switched to TCP/IP and the internet went operational. She was a remarkable person.

Listening to it, and thinking about the audience of NSA engineers, I wonder how much of what she’s talking about as the future of computing—miniaturization, parallelization—was being done in the present and in secret.

US Federal Court Rules Against Geofence Warrants

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/08/us-federal-court-rules-against-geofence-warrants.html

This is a big deal. A US Appeals Court ruled that geofence warrants—these are general warrants demanding information about all people within a geographical boundary—are unconstitutional.

The decision seems obvious to me, but you can’t take anything for granted.

How A/B Testing and Multi-Model Hosting Accelerate Generative AI Feature Development in Amazon Q

Post Syndicated from Sai Srinivas Somarouthu original https://aws.amazon.com/blogs/devops/how-a-b-testing-and-multi-model-hosting-accelerate-generative-ai-feature-development-in-amazon-q/

Introduction

In the rapidly evolving landscape of Generative AI, the ability to deploy and iterate on features quickly and reliably is paramount. We, the Amazon Q Developer service team, relied on several offline and online testing methods, such as evaluating models on datasets, to gauge improvements. Once positive results are observed, features were rolled out to production, introducing a delay until the change affected 100% of customers.

This blog post delves into the impact of A/B testing and Multi-Model hosting on deploying Generative AI features. By leveraging these powerful techniques, our team has been able to significantly accelerate the pace of experimentation, iteration, and deployment. We have not only streamlined our development process but also gained valuable insights into model performance, user preferences, and the potential impact of new features. This data-driven approach has allowed us to make informed decisions, continuously refine our models, and provide a user experience that resonates with our customers

What is A/B Testing?

A/B testing is a controlled experiment, and a widely adopted practice in the tech industry. It involves simultaneously deploying multiple variants of a product or feature to distinct user segments. In the context of Amazon Q Developer, the service team leverages A/B testing to evaluate the impact of new model variants on the developer experience. This helps in gathering real-world feedback from a subset of users before rolling out changes to the entire user base.

  1. Control group: Developers in the control group continue to receive the base Amazon Q Developer experience, serving as the benchmark against which changes are measured.
  2. Treatment group: Developers in the treatment group are exposed to the new model variant or feature, providing a contrasting experience to the control group.

To run an experiment, we take a random subset of developers and evenly split it into two groups: The control group continues to receive the base Amazon Q Developer experience, while the treatment group receives a different experience.

By carefully analyzing user interactions and telemetry metrics of the control group and comparing them to those from the treatment group, we can make informed decisions about which variant performs better, ultimately shaping the direction of future releases.

How do we split the users?

Whenever a user request is received, we perform consistent hashing on the user identity and assign the user to a cohort. Irrespective on which machine the algorithm runs, the user will be assigned the same cohort. This means that we can scale horizontally – user A’s request can be served by any machine and user A will always be assigned to group A from the beginning to the end of the experiment.

Individuals in the two groups are, on average, balanced on all dimensions that will be meaningful to the test. This means that we do not expose a cohort to have more than one experiment at any given time. This enables us to conduct multivariate experiments where one experiment does not impact the result of another.

The diagram illustrates how a consistent hashing algorithm based on userID’s assigns users to cohorts representing control or treatment groups of experiments.

The above diagram illustrates the process of user assignment to cohorts in a system conducting multiple parallel A/B experiments.

How do we enable segmentation?

For some A/B experiments, we want to perform A/B experiments for users matching certain criteria. Assume we want to exclusively target Amazon Q Developer customers using the Visual Studio Code Integrated Development Environment (IDE). For such scenarios, we perform cohort allocation only for users who meet the criteria. In this example, we would divide a subset of Visual Studio Code IDE users into control and treatment cohorts.

How do we route the traffic between different models ?

Early on, we realized that we will need to host hundreds of models. To achieve this, we run multiple Amazon Elastic Container Service (Amazon ECS) clusters to host different models. We leverage Application Load Balancer’s path based routing to route traffic to the various models.

The diagram depicts how Application Load Balancer paths 1-n direct traffic to control model or treatment model 1-n.

The above diagram depicts how Application Load Balancer redirects traffic to various models based on path-based routing. Where path1 is routing to control model and path2 is routing to treatment model 1 etc.

How do we enable different IDE experiences for different groups?

The IDE plugin polls the service endpoint asking if the developer belongs to the control or treatment group. Based on the response the user will be served the control or treatment experience.

The diagram shows the IDE plugin polling the backend service to display a control or treatment experience.

The above diagram depicts how the IDE plugin provides different experience based on control or treatment group.

How do we ingest data?

From the plugin, we publish telemetry metrics to our data plane. We honor opt-out settings of our users. If the user is opted-out, we do not store their data. In the data plane, we check the cohort of the caller. We publish telemetry metrics with cohort metadata to Amazon Data Firehose, which delivers the data to an Amazon OpenSearch Serverless destination.

The diagram depicts the flow of data from IDE to Data Plane to Kinesis Data Firehose to Amazon OpenSearch Serverless.

The above diagram depicts how metrics are captured via the data plane into Amazon OpenSearch Serverless.

How do we analyze the data?

We publish the aggregated metrics to OpenSearch Serverless. We leverage OpenSearch Serverless to ingest and index various metrics to compare and contrast between control and treatment cohorts. We enable filtering based on metadata such as programming language and IDE.

Additionally, we publish data and metadata to a data lake to view, query and analyze the data securely using Jupyter Notebooks and dashboards. This enables our scientists and engineers to perform deeper analysis.

Conclusion

This post has focused on challenges Generative AI services face when it comes to fast experimentation cycles, the basics of A/B testing and the A/B testing capabilities built by the Amazon Q Developer service team to enable multi-variate service and client-side experimentation. We can gain valuable insights into the effectiveness of the new model variants on the developer experience within Amazon Q Developer. Through rigorous experimentation and data-driven decision-making, we can empower teams to iterate, innovate, and deliver optimal solutions that resonate with the developer community.

We hope you are as excited as us about the opportunities with Generative AI! Give Amazon Q Developer and Amazon Q Developer Customization a try today:

Amazon Q Developer Free Tier: https://aws.amazon.com/q/developer/#Getting_started/

Amazon Q Developer Customization: https://docs.aws.amazon.com/amazonq/latest/qdeveloper-ug/customizations.html

About the authors

Sai Srinivas Somarouthu

Sai Srinivas Somarouthu is a Software Engineer at AWS, working on building next generation models and development tools such as Amazon Q. Outside of work, he finds joy in traveling, hiking, and exploring diverse cuisines.

Karthik Rao

Karthik is a Senior Software Engineer at AWS, working on building next generation development tools such as Amazon Q. Outside of work, he can be found hiking and snowboarding.

Kenneth Sanchez

Kenneth is a Software Engineer at AWS, working on building next generation development tools such as Amazon Q. Outside of work, he likes spending time with his family and finding new good places to drink coffee.

Вода в чешмите на селата от Родопи няма, но проблемът не е в липсата на дъжд

Post Syndicated from VassilKendov original https://kendov.com/%D0%B2%D0%BE%D0%B4%D0%B0-%D0%B2-%D1%87%D0%B5%D1%88%D0%BC%D0%B8%D1%82%D0%B5-%D0%BD%D0%B0-%D1%81%D0%B5%D0%BB%D0%B0%D1%82%D0%B0-%D0%BE%D1%82-%D1%80%D0%BE%D0%B4%D0%BE%D0%BF%D0%B8-%D0%BD%D1%8F%D0%BC%D0%B0/

Вода в чешмите на селата от Родопи няма, но проблемът не е в липсата на дъжд.

Много се е изписало за Маите. Тяхната цивилизация все още крие тайните си, макар някои обичаи да са доста добре изследвани.
При тях решението на всеки природен проблем се е свеждал до жертвоприношения. При продължителна суша например, владетелите са имали задачата да измолят дъжд от боговете. Те на свой ред са прехвърляли топката върху поданиците и са организирали публични жертвоприношения. В една от свещените пещери в Чечен Ица, където хвърляли телата от жертвоприношенията са намерени 127 тела, като 80% от тях са били момчета на възраст от 3 до 11 години. Лично мое предположение е, е това са били деца на политически опоненти.

Какво обаче се е случвало, когато владетелите не са успявали да измолят дъжд от боговете?
Ами много просто – пренасяли са в жетртва владетелите и техните семейства, и са избирали нов владетел.
Нищо не искам да кажа, но мисля че доста мъдър народ са били Маите. Затова и до ден днешен се възхищаваме на достиженията на цивилизацията им.

Да видим сега как ние с нашите достижения 1000 години след тях би следвало да се справим с липсата на вода в 21 век.

Тръбите не се виждат и не стават за PR

Може би едина от най-важните предпоставки за да не се реши проблемът с водата е, че тръбите са под земята и не се виждат. От друга страна копането и затваряне на улици създава доста неприятности на населението, а това не е добре. Всички знаем колко е важен PR-а за кмета на Община Родопи. Друго си е да е лапма, или улица, или някоя обновенна сграда… Вървиш си и се блъскаш в нея ежедневно. Няма как да не я видиш. Пък си речеш «Добър си ни е Кмета. Я виж колко неща прави неща за селото.» А водата? Те дъждовете като дойдат, всичко ще се оправи.
Хубаво ама така е от 5 години.

Администрацията няма проблем с водата

Служителите в Община Родопи до един имат жилища в Пловдив. А в Пловдив проблем с водата няма.
Злите езици говорят, че председателят на Общинския съвет г-н Владо Маринов, който живее в с. Бойково, нямал проблем с водата в къщата си за гости. Да но останалите в село Бойково имат такъв проблем всяко лято.
Аз самият съм жител на Бойково. Миналата неделя се разходих по планината над селото и стигнах до съседното село – Ситово. И то няма вода. Чешмите в гората обаче всичките бликат от вода. Явно вода има и дъждът не е фактор. Позагледах и старите каптажи (защото направиха нови преди години). Ами имат си вода, даже някои преливат. Откъдето и да го погледна, вода в гората има предостатъчно. В селата обаче няма, което ме навежда на друга мисъл.


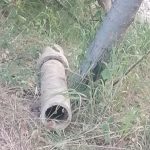
Специално в Бойково загледах тръбите на каптажите, които водят към селото. Ами теснички са и са стари. Прди 2 седмици, докато пооправяха горския път за селския събор, спукаха тръбата и сега се вижда над земята. Според мен е 1.5 цола, но не мога да се закълна. Не носех шублер да я измеря. А ВиК мрежата в Бойково беше сменена преди години с изцяло нови тръби, които сад доста по-широки от тези, които доставят водата от каптажа. Колко са затлачени това е отделен въпрос. Знам обаче, че ВиК искат да им се отчужди право на преминаване или собственост върху земята, през които минават тръбите от каптажите, за да ги сменят. И са си прави. Много от тръбите минават през частни имоти, защото са правени по комунизма. Как си представяте ВиК да копае в частен имот?

И тук зачитаме закона за водите

чл.10 ал.4 (2) Политиката по експлоатация и реконструкция на В и К инфраструктурата се осъществява от кмета на общината.

ал. 1 Общинският съвет приема Програма за развитието на В и К сектора

ал. 2 Кметът на общината разработва Програмата и я предлага за обществено обсъждане.

И щом законът е такъв, продължаваме да търсим да видим какво пак не е свършила общината


Заделените пари в бюджета реално не се използват

В заседанията по обсъждането на бюджета, почти винаги съм сам. С малки изключения. Помня как жители на с. Марково, организирани от кмета г-жа Терзиева, дойдоха на такова заседание и съответно получиха най-голям дял от парите по изтегления кредит, за ремонт на няколко улици в селото.
Нищо, че всички ще плащат кредита, парите отиват в Марково.

ТАКА И ТРЯБВА ДА БЪДЕ! – Парите трябва да следват инициативните!

Да обаче и в Марково вече има режим на водата. Не ми се рови отново в бюджета (ако някои си плати ще му го изровя разбира се), но в последните бюджети имаше заложени капиталови разходи за водни колектори, които да решат проблема с водата в Марково. И така няколко години. Земята била отредена, проект по думите на кмета Михайлов имало, но колекторите нещо ги няма.
Всички знаем колко е сложна работата на кмета, но пък според закона по-горе, политиката по водата се осъществява от него. Това му е работата. Би следвало да е и приоритет. Много хубаво, че имаме LED лампи или тържества с хора във всяко село, ама водата…

Може би малко хора знаят, че акведуктът на Коматевския възел в Пловдив е захранвал Тримонциум с вода точно от землището на Марково. Тогава в Тримонциум по оценки на историци са живели между 60-80 000 души.
В днешното село Марково живет около 5500 души. Разбира се това са хора с много по-голямо потребление на вода от средния жител в древен Тримонциум. В селото има множество къщи с басейни и морави, изискващи напояване, така че потребленито не вода на тези 5500 може и да е по-голямо от това на древните жители, ако и да са били над 60 000 души.
Но и другото е вярно. Днес не строим акведукти, а полагаме тръби в дупки, изкопани с фадроми и багери. Загубите на вода би следвало да са много по-малко в сравнение с акведукта, а водита може да се пренася от много километри, благодарение на електричество и помпени станции.

Може ама някой трябва да има визията да го направи, а 5 години явно не са достаъчни за тази визия в Община Родопи. Не са римляни все пак и са тук само до следващите избори.

Ръстът в населението

Ето какво казва г-жа Терзиева, кмет на с. Марково

„”Признанието е голямо, това е много важен приз за всеки общественик, който е решил да извършва дейност за благото на хората. Марково е една кауза. Доста се разраства селото, в него вече има около 5500 жители. Тенденцията в последните 4-5 години е такава – младите семейства да отиват в населени места близо до големия град. Марково се намира на само 5 км от Пловдив, което го прави притегателно място”, заяви Терзиева пред Bulgaria ON AIR.“

Мисля, че ако синът ми в 6-ти клас прочете тези редове, веднага ще разбере, че инфраструктурата няма да издържи това развитие и трябва да се направят инвестиции за подобрението. За общинската администрация не мога да гаранирам какви изводи си правят от тази информация.

И понеже инвестициите изискват средства, отиваме на следващия очевидно нерешим проблем

Колко пари трябват, откъде да дойдат и какво пропуснахме

На този въпрос не мога да отговоря на прима виста. Мога да предполагам обаче.
От опит знам, че смяната на канализацията на едно село като Марково, ще струва около 30 млн. лева. Отделно пречиствателна станция. Последният бюджет на Община Родопи за 2024 е 52.5 млн.

С две думи без кредит или заем проблемът с доставката на вода няма да се реши. Просто не е по силите на Община Родопи. Нито финансово, нито административно, както е видно.

Селата от Община Родопи се водоснабдяват от ВиК Пловдив. Самия Пловдив е около 500 000 хиляди, но няма проблем с водата. Бюджетът им обач е 684 милиона. Възможностите им за получаване на кредит съответно също са 10 пъти по-добри от тези на Община Родопи.
Друг е въпросът, че Община Родопи похарчи кредита не за водна инфраструктура, а за лампи и пътища. Няма лошо разбира се, но така унищожава възможността за получаване на кредит за ВиК инфраструктура.

Сега вече би трябвало хората да научат думата „ПРИОРИТЕТ“ в харчовете. Ясно е, че улиците и лампите се виждат, ама не се пият. По лош път мога да се движа, със стара лампа мога да се осветявам, ама без вода в чешмата… Направо да хващаме коритата и на ходим да перем на реката. Администрацията на общината няма да ги мислим, те си отиват в Пловдив, а там всичко си има.

И тук един риторичен въпрос към жителите на с. Белащица „-Как очаквате пари за инфраструктура с бюджета на Община Родопи? Нали не искахте в пределите на Пловдив?“

Политическата страна на нещата

Ако трябва да падна на нивото на Общинската администрация, бих попитал съвсем по герберски „-И как очаквате да Ви дадем държавни пари за ВиК, като сте си избрали кмет комунист?“
Парите знаете, че не достигат никога. В положението на селата от Община Родопи са стотици други села с кметове близки до властта. На кое село да оправим водата по-напред? На Брестовица (с кмет комунист) или някое друго с кмет лоялен към друга политическа сила?

За финал ще съм доволен, ако в главите на хората остане схващането, че решението на проблема с водата не е еднократен акт. Трябват много предпоставки за да се случи. Този порядък за мен е най-добрия

Гласувате за хора с визия – Ходите на заседанията на Общински съвет и си задавате въпросите, колкото и да са неудобни – Обединявате се около хора с визия, а не с PR мания – Организирате протести пред Общна Родопи – Не си мълчите, когато в социалните мрежи бушуват тролове и се опитват да ви замазват очите.

Иначе и обичаят “Бяла пеперуда” върши работа до следващото лято, когато проблемът ще е същият.

Васил Кендов – жител на безводно Бойково

Моля използвайте приложената форма за записване на час за среща
[contact-form-7]

The post Вода в чешмите на селата от Родопи няма, но проблемът не е в липсата на дъжд appeared first on Kendov.com.

Story of an Undercover CIA Agent who Penetrated Al Qaeda

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/08/story-of-an-undercover-cia-agent-who-penetrated-al-qaeda.html

Rolling Stone has a long investigative story (non-paywalled version here) about a CIA agent who spent years posing as an Islamic radical.

Unrelated, but also in the “real life spies” file: a fake Sudanese diving resort run by Mossad.

Hacking Wireless Bicycle Shifters

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/08/hacking-wireless-bicycle-shifters.html

This is yet another insecure Internet-of-things story, this one about wireless gear shifters for bicycles. These gear shifters are used in big-money professional bicycle races like the Tour de France, which provides an incentive to actually implement this attack.

Research paper. Another news story.

Slashdot thread.

The State of Ransomware

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/08/the-state-of-ransomware.html

Palo Alto Networks published its semi-annual report on ransomware. From the Executive Summary:

Unit 42 monitors ransomware and extortion leak sites closely to keep tabs on threat activity. We reviewed compromise announcements from 53 dedicated leak sites in the first half of 2024 and found 1,762 new posts. This averages to approximately 294 posts a month and almost 68 posts a week. Of the 53 ransomware groups whose leak sites we monitored, six of the groups accounted for more than half of the compromises observed.

In February, we reported a 49% increase year-over-year in alleged victims posted on ransomware leak sites. So far, in 2024, comparing the first half of 2023 to the first half of 2024, we see an even further increase of 4.3%. The higher level of activity observed in 2023 was no fluke.

Activity from groups like Ambitious Scorpius (distributors of BlackCat) and Flighty Scorpius (distributors of LockBit) has largely fallen off due to law enforcement operations. However, other threat groups we track such as Spoiled Scorpius (distributors of RansomHub) and Slippery Scorpius (distributors of DragonForce) have joined the fray to fill the void.

Friday Squid Blog: The Market for Squid Oil Is Growing

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/08/friday-squid-blog-the-market-for-squid-oil-is-growing.html

How did I not know before now that there was a market for squid oil?

The squid oil market has experienced robust growth in recent years, expanding from $4.56 billion in 2023 to $4.94 billion in 2024 at a compound annual growth rate (CAGR) of 8.5%. The growth in the historic period can be attributed to global market growth, alternative to fish oil, cosmetics and skincare industry, sustainability practices, regulatory influence.

Blog moderation policy.

New Windows IPv6 Zero-Click Vulnerability

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/08/new-windows-ipv6-zero-click-vulnerability.html

The press is reporting a critical Windows vulnerability affecting IPv6.

As Microsoft explained in its Tuesday advisory, unauthenticated attackers can exploit the flaw remotely in low-complexity attacks by repeatedly sending IPv6 packets that include specially crafted packets.

Microsoft also shared its exploitability assessment for this critical vulnerability, tagging it with an “exploitation more likely” label, which means that threat actors could create exploit code to “consistently exploit the flaw in attacks.”

Details are being withheld at the moment. Microsoft strongly recommends patching now.

NIST Releases First Post-Quantum Encryption Algorithms

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/08/nist-releases-first-post-quantum-encryption-algorithms.html

From the Federal Register:

After three rounds of evaluation and analysis, NIST selected four algorithms it will standardize as a result of the PQC Standardization Process. The public-key encapsulation mechanism selected was CRYSTALS-KYBER, along with three digital signature schemes: CRYSTALS-Dilithium, FALCON, and SPHINCS+.

These algorithms are part of three NIST standards that have been finalized:

NIST press release. My recent writings on post-quantum cryptographic standards.

EDITED TO ADD: Good article:

One – ML-KEM [PDF] (based on CRYSTALS-Kyber) – is intended for general encryption, which protects data as it moves across public networks. The other two –- ML-DSA [PDF] (originally known as CRYSTALS-Dilithium) and SLH-DSA [PDF] (initially submitted as Sphincs+)—secure digital signatures, which are used to authenticate online identity.

A fourth algorithm – FN-DSA [PDF] (originally called FALCON) – is slated for finalization later this year and is also designed for digital signatures.

NIST continued to evaluate two other sets of algorithms that could potentially serve as backup standards in the future.

One of the sets includes three algorithms designed for general encryption – but the technology is based on a different type of math problem than the ML-KEM general-purpose algorithm in today’s finalized standards.

NIST plans to select one or two of these algorithms by the end of 2024.

IEEE Spectrum article.

Slashdot thread.

Achieving Frugal Architecture using the AWS Well-Architected Framework guidance

Post Syndicated from Ashley DeLoach original https://aws.amazon.com/blogs/architecture/achieving-frugal-architecture-using-the-aws-well-architected-framework-guidance/

As part of the re:Invent 2023 keynote, Dr. Werner Vogels introduced the Frugal Architect mindset. This mindset emphasizes the importance of continuous learning, curiosity, and regular revision of architectural choices with a focus on cost and sustainability. Cost and sustainability should be treated as critical non-functional requirements, alongside factors like security, compliance, and performance. The Frugal Architect approach involves measuring and optimizing cost at every stage of the development process, which allows for innovation in parallel with promoting responsible resource usage. In the rapidly-evolving technology landscape, builders should adopt the Frugal Architect mindset to balance innovation with cost efficiency and environmental sustainability.

This blog discusses how the six pillars of the AWS Well-Architected Framework (operational excellence, security, reliability, performance efficiency, cost optimization, and sustainability) align with the seven Frugal Architect laws. It demonstrates how adhering to the principles and best practices outlined in these pillars can help architects and builders effectively implement the Frugal Architect laws in their projects. The Well-Architected Framework provides a comprehensive set of guidelines that embed the concepts of frugality, efficiency, and cost effectiveness, which are the core tenets of the Frugal Architect laws. By following the Framework’s pillars, architects can build secure, reliable, efficient, and cost-optimized systems and promote sustainability.

Make Cost a Non-functional Requirement (Law 1)

Non-functional requirements are criteria that evaluate a system’s operation instead of its specific features or functionality. This includes aspects like accessibility, availability, scalability, security, portability, maintainability, and compliance. However, one crucial non-functional requirement that is often overlooked is cost. Consider implications early on and throughout the design, development, and operation of your systems. Organizations can strike a balance between desired features, time-to-market, and operational efficiency through early prioritization of cost considerations. The Frugal Architect argues that you should treat cost as a fundamental non-functional requirement that should be given upfront consideration when planning and initiating system development projects.

The Cost Optimization Pillar of the AWS Well-Architected Framework provides guidance on how to optimize costs when using AWS Cloud services. It emphasizes treating cost as a key requirement, not an afterthought. The main principles focus on the importance of a robust financial management processes, adoption of a cloud consumption model that allows for flexible scaling and pay-per-use billing, continual measurement of outputs against costs to optimize efficiency, use of managed services to minimize operational overhead, and implementation of transparent cost attribution to tie cloud spending to revenue sources and workloads. Organizations that follow these practices can effectively manage and optimize their costs and benefit from the scalability and agility of cloud computing.

These cost optimization principles can help organizations maximize the financial benefits of using the AWS Cloud and avoid wasteful spending. Cost optimization is an ongoing process that includes rightsizing, higher output for the same cost, and use of the most cost-effective AWS services. The pillar promotes a disciplined approach to evaluate trade-offs between cost and other optimization areas like performance or reliability. Overall, you can use this pillar to make informed decisions to provision and operate AWS services cost-effectively.

Systems that Last Align Cost to Business (Law 2)

The durability and longevity of a system are closely tied to how well its costs align with the underlying business model. During the creation of a system, consider revenue sources and profit drivers. The key is to identify the primary dimension or aspect that generates revenue, and then verify that the system architecture supports and optimizes for that revenue-generating dimension. Essentially, revenue and profitability considerations should be the primary forces behind cost decisions in system design.

The AWS Well-Architected Cost Optimization Pillar provides practices and guidance for organizations to accurately monitor their AWS costs and usage. This visibility helps users understand the profitability of different business units and products, which facilitates informed decisions on resource allocation across the organization. Organizations can implement these practices to gain insights into their AWS spending patterns, which aids in development of effective cost optimization strategies. Overall, accurate expenditure analysis and attribution are crucial for organizations to optimize cloud costs, measure ROI, and make data-driven resource allocation decisions.

It’s important to accurately identify and attribute cloud costs to specific workloads. The cloud allows for transparent cost attribution, which helps organizations link costs to individual revenue streams and workload owners. This granular cost attribution data empowers workload owners to measure return on investment (ROI) for their workloads. With detailed cost information, workload owners can optimize resource utilization and reduce costs by rightsizing resources, eliminating waste, and making informed decisions. Organizations must use accurate cost attribution to understand where their cloud spending is going and verify that resources are being used efficiently across different workloads and revenue streams.

Architecting is a Series of Trade-Offs (Law 3)

Architectural decisions involve trade-offs, particularly between cost, resilience, and performance. Systems will inevitably fail, so investment in resilience is important but may impact performance. It’s important to find the right balance between technical requirements and business needs and align with risk tolerance and budget constraints. Frugality is about maximizing value, not just minimizing spend. Frugality means that you determine what you’re can pay for based on your priorities and make informed trade-off decisions. Ultimately, architectural choices require careful consideration of the tensions between different non-functional requirements.

The AWS Well-Architected Framework helps you make architectural trade-offs through its design principles and practices across its six pillars with your business requirements in mind. As you architect workloads, you make trade-offs between pillars based on your business context. You might optimize to improve the sustainability impact and reduce cost at the expense of reliability in development environments, or for mission-critical solutions. You might optimize reliability with increased costs and sustainability impact. In ecommerce solutions, performance can affect revenue and customer propensity to buy. Security generally is not a viable trade-off against the other pillars.

Rather than optimizing for any single pillar, the Framework guides a holistic evaluation across all pillars to determine the right architectural approach. Organizations can use AWS best practices while they find the optimal balance that aligns with their unique requirements. The key is making intentional trade-off decisions instead of following any uniform approach.

Unobserved Systems Lead to Unknown Costs (Law 4)

Without proper observation and measurement, the true operational costs of a system remain hidden, and wasteful practices can persist unnoticed. Just as exposing a utility meter prompts more mindful usage, visibility increases into costs can drive more sustainable behaviors. While implementing comprehensive monitoring requires upfront investment, the long-term benefits of conserving resources and optimizing efficiency make it a worthwhile endeavor. Ultimately, you should maintain cost awareness to foster a culture of responsible, sustainable practices.

The Operational Excellence Pillar of the AWS Well-Architected Framework emphasizes the importance of observability to gain actionable insights into workloads. This involves creation of key performance indicators (KPIs) and use of observability data telemetry to comprehensively understand workload behavior, performance, reliability, cost, and health. Organizations can implement observability best practices to make informed decisions and take prompt action when business outcomes are at risk due to issues with workload operation. Observability data provides visibility into the current state and helps identify areas for improvement. This means that organizations can be proactive in performance optimization, reliability enhancement, and cost reduction based on the actionable insights derived from observability telemetry data. Overall, observability is crucial for maintenance of operational excellence through the use of data-driven decision-making and continuous improvement of workloads.

Overall, monitoring guidance is a core component across multiple pillars of the Well-Architected Framework, as it helps organizations effectively manage and optimize their cloud workloads. For more detail on the monitoring principles of the AWS Well-Architected Framework, see Cost-Aware Architectures Implement Cost Controls (Law 5).

Cost-Aware Architectures Implement Cost Controls (Law 5)

The key aspects of frugal architecture combine granular controls with robust monitoring to identify areas for optimization. This helps you optimize costs and maintain a good user experience. With a robust monitoring system, you can take action where improvements are needed.

The AWS Well-Architected Framework aligns with the concept of frugality, which focuses on maximizing value rather than just minimizing spending. The Framework helps businesses achieve maximum value by making architectural choices that meet their specific requirements.

The Cost Optimization Pillar emphasizes the continual monitoring of usage and costs to identify opportunities for efficiency improvements and cost savings. This includes expenditure analysis, adoption of consumption-based models, and implementation of cloud financial management practices.

The Security Pillar, Reliability Pillar, and Performance Efficiency Pillar reinforce the importance of monitoring systems, workloads, and costs in real-time to maintain security, automatically recover from failures, and optimize performance relative to cost.

The Sustainability Pillar focuses on measurement of a workload’s current and forecasted environmental impact. It recommends continual evaluation of new hardware and software offerings that can reduce the environmental footprint.

Overall, monitoring guidance spans multiple Well-Architected pillars to maximize value through optimization of cost, performance, security, reliability, and sustainability.

Cost Optimization is Incremental (Law 6)

Cost efficiency is a continuous process, not a one-time goal. Regularly monitor your systems to identify inefficient patterns and areas for optimization. Revisit and refine systems periodically to find additional opportunities for improvement and further reduce costs over time.

The Cost Optimization Pillar covers principles like analysis and attribution of expenditure, measurement of overall efficiency, adoption of a consumption model, and implementation of cloud financial management practices.

Additionally, the Operational Excellence Pillar provides principles that apply not just to cost optimization but all pillars. These include observability for actionable insights, safe automation where possible, frequent small reversible changes, frequent refinement of operations procedures, anticipation of failure, and documentation and distribution of learning from operational events and metrics.

Organizations can follow these AWS Well-Architected Framework principles and their practices to continuously improve their cloud architectures and operations and optimize costs effectively.

Unchallenged Success Leads to Assumptions (Law 7)

We should continue to reevaluate past approaches, even those that were previously successful. Just because something worked before does not mean that it is still the best method. Grace Hopper, a computer scientist, mathematician, and United States Navy rear admiral, cautioned against blind adherence to tradition, saying that “we’ve always done it this way” is a dangerous mindset. We must be willing to question the old ways and explore new and potentially better methods.

The AWS Well-Architected Framework advocates for an evolutionary architecture approach to system design. Traditional architectures are often designed as static, with only a few major version updates during the system’s lifetime. However, as businesses and requirements change over time, initial architectural decisions can limit the ability to adapt and evolve the system. Cloud computing enables capabilities like automated testing and lower-risk design changes, which allows systems to evolve continually rather than being constrained by the original design. An evolutionary architecture positions businesses to take advantage of new innovations and changes as part of standard practice. Rather than being locked into original architectural choices, an evolutionary approach fosters ongoing adaptation and modernization as requirements shift. This contrasts with traditional fixed architectures that make it difficult to evolve over time and provides greater flexibility to evolve systems iteratively.

The Operational Excellence Pillar includes implementation of observability to understand system behavior, safe automation of processes, frequent but reversible changes, regular refinement of operations procedures, proactive anticipation potential failures proactively, and distribution of learnings from operational events and metrics to drive continuous improvement.

Overall, the Well-Architected Framework provides guidance on evolutionary architecture and operations processes to effectively manage increasing software complexity over time.

Conclusion

Frugality is about maximizing value, rather than just minimizing costs. Following AWS Well-Architected Framework best practices regarding security, reliability, and operational excellence can help realize frugal yet robust architectures. True frugality involves optimizing costs by aligning spending with areas that deliver the highest business value and impact. The Well-Architected Framework provides guidance for making architectural decisions that increase efficiency, lower risks, and maximize return on cloud investments. This involves determining priorities, understanding sources of value, and making informed trade-off decisions based on those priorities. It’s important to avoid indiscriminate cost-cutting and instead focus on resources on what matters most to drive value for the organization. By following Well-Architected best practices, companies can practice frugality in a strategic way that balances optimization with business goals.

Start your Frugal Architecture journey with AWS Well-Architected today by reading the documentation or visiting the AWS Well-Architected Tool in the console.

Texas Sues GM for Collecting Driving Data without Consent

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/08/texas-sues-gm-for-collecting-driving-data-without-consent.html

Texas is suing General Motors for collecting driver data without consent and then selling it to insurance companies:

From CNN:

In car models from 2015 and later, the Detroit-based car manufacturer allegedly used technology to “collect, record, analyze, and transmit highly detailed driving data about each time a driver used their vehicle,” according to the AG’s statement.

General Motors sold this information to several other companies, including to at least two companies for the purpose of generating “Driving Scores” about GM’s customers, the AG alleged. The suit said those two companies then sold these scores to insurance companies.

Insurance companies can use data to see how many times people exceeded a speed limit or obeyed other traffic laws. Some insurance firms ask customers if they want to voluntarily opt-in to such programs, promising lower rates for safer drivers.

But the attorney general’s office claimed GM “deceived” its Texan customers by encouraging them to enroll in programs such as OnStar Smart Driver. But by agreeing to join these programs, customers also unknowingly agreed to the collection and sale of their data, the attorney general’s office said.

Press release. Court filing. Slashdot thread.