Tag Archives: ransomware

2025 Ransomware: Business as Usual, Business is Booming

Post Syndicated from Chris Boyd original https://blog.rapid7.com/2025/04/08/2025-ransomware-business-as-usual-business-is-booming/
2025 Ransomware: Business as Usual, Business is Booming

Getting an edge on your adversaries involves understanding their behaviors and their mindset. Rapid7 Labs took a look at internal and publicly-available ransomware data for Q1 2025 and added our own insights to provide a picture of the year thus far—and what you can do now to reduce your attack surface against ransomware.

The data highlights that businesses can’t afford to take their foot off the gas pedal when it comes to proactively tackling ransomware. Established threat actors and relative newcomers are taking an “if it ain’t broke, don’t fix it” approach, shunning unpredictability for proven revenue generation techniques. And, in almost all cases, the name of the game is data exfiltration and blackmail via leak site posts.

At a glance

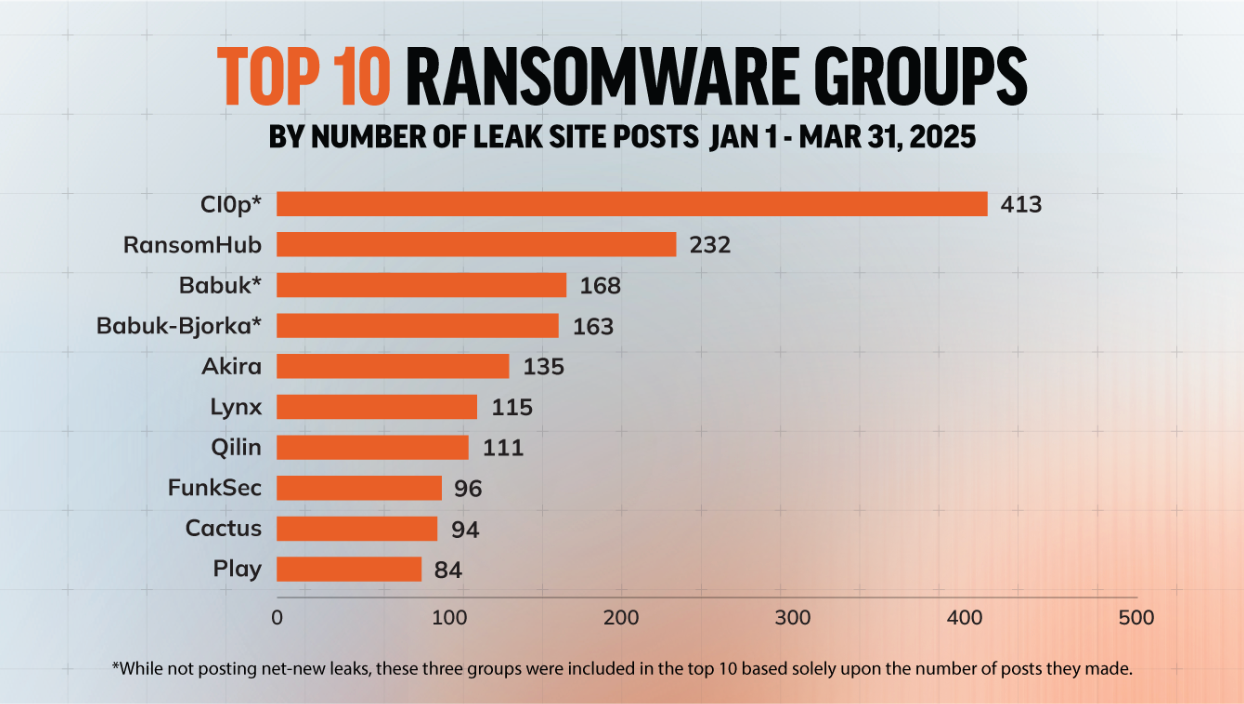
The heavy hitters of the current ransomware landscape are a mixture of new and familiar faces, largely leaning into the affiliate model or announcing partnerships with well-known groups for a visibility boost. There were 80 active groups in Q1, 16 of them new since January 1. There are also 13 groups that were active in Q4, 2024, but have thus far been silent in 2025.
2025 Ransomware: Business as Usual, Business is Booming

New ransomware groups active since the start of 2025 include (but are not limited to): Ailock, Belsen Group, CrazyHunter, Cs-137, D0Glun, GD LockerSec, Linkc, NightSpire, Ox Thief, Run Some Wares, SECP0, Sonshi, and VanHelsing.

Popular targets in Q1:

  • Manufacturing, business services, healthcare, and construction were the top industries under siege by a variety of established and newly emerging threat actors. Of the 618 leak site posts we reviewed containing victims’ industry information, 22% were manufacturing organizations. Business services was a distant second at 11%, followed by healthcare services and construction, both at 10%.
  • Top regional targets included traditional favorites such as the U.S., Canada, the UK, Germany, and Australia, as well as a fair share of victims in Taiwan, Singapore, and Japan. We also saw an increase of victims in unusual locations such as Colombia and Thailand.

Reinvested ransoms

The Black Basta chat leaks that occurred in February provided an insightful look into not only the group’s infighting, but also its inner workings. And while the group’s activity stopped dead in its tracks (the last leak site post was on January 11, 2025), we would be remiss if we didn’t give mention to a significant trend we have suspected was happening, but were only able to verify with these chat logs: Ransomware groups are reinvesting the ransoms they’re paid to purchase zero days.

Within the Black Basta chat logs, we observed that on November 23, 2023, the group was offered a zero-day exploit targeting Ivanti Connect Secure for their purchase. The exploit came with an asking price of $200,000, and is described by the seller as an unauthenticated RCE exploit, leveraging an unknown memory corruption vulnerability.

While it’s unclear if a purchase was ever made, we can speculate as to what this vulnerability may or may not have been, based on recently published Ivanti Connect Secure CVEs. There were three notable CVEs exploited in the wild as zero days circa late 2023: CVE-2023-46805, CVE-2024-21887, and CVE-2024-21893. However, the seller describes the zero day as a memory corruption vulnerability, which none of those three were. It was also not CVE-2024-21893, which was an SSRF vulnerability. A more recent CVE affecting Ivanti Connect Secure, which was both a memory corruption vulnerability, and exploited in the wild as a zero day, was CVE-2025-0282; however, the affected version ranges of this CVE don’t line up with the zero day being offered in the Black Basta logs. It is possible the zero day being offered for sale to the Black Basta group remains a zero day, as there is no evidence to suggest that it has been patched.

Separate from the Ivanti discussion, however, we observed that Black Basta did indeed buy a Juniper firewall exploit. This followed a comparison between a public, authenticated remote code execution (RCE) exploit (which only gives user-mode access) and the purchased one that provides full root access.

Repackaged offerings

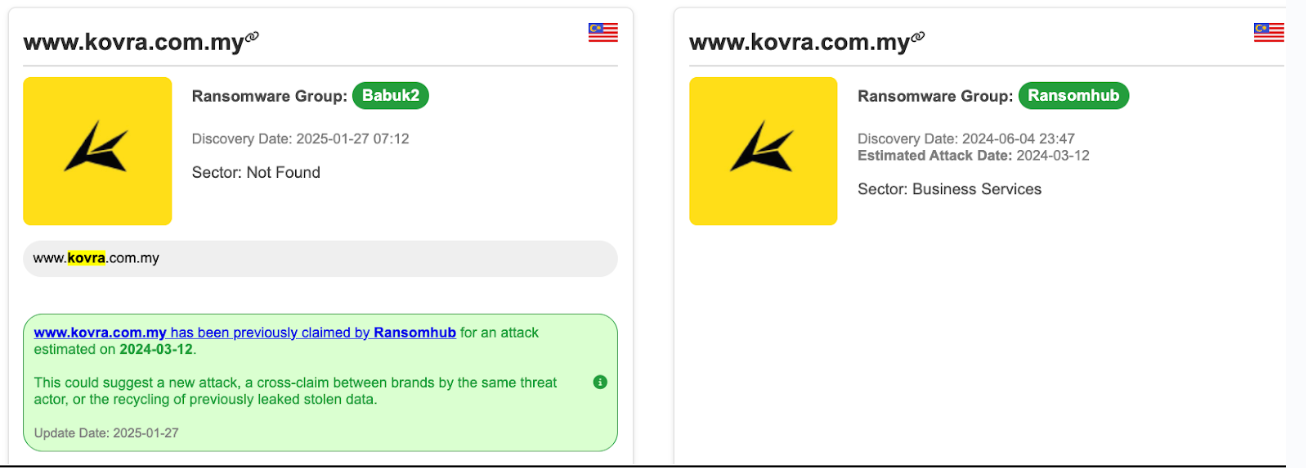
Several groups are making a name for themselves by simply dragging out the classics. Most recently, a supposedly resurrected Babuk ransomware group was not all it seemed, with old data taken from RansomHub, FunkSec and LockBit repurposed as their own. Rapid7 analysis highlights the challenges of groups reforming or collaborating under new identities, such as “Babuk 2.0” just being LockBit 3.0 / LockBit Black with a different name applied.

Elsewhere, FunkSec is not above repurposing old leak data, and LockBit was found to be posting a mixture of old data and faked attacks after global arrests of suspected LockBit developers and affiliates. Visibly weakened by the trilateral law enforcement action, what was left of LockBit turned to fakery as a way of making it seem as though things were still business as usual.

Restructured groups

When ransomware groups go silent, others are there to take their place. Part of this dynamic is a continuously circulating affiliate network that keeps defenders and cybersecurity analysts on their toes. Rebrands aside, Rapid7 observed what appears to be a “changing of the guard” within the Akira ransomware group.

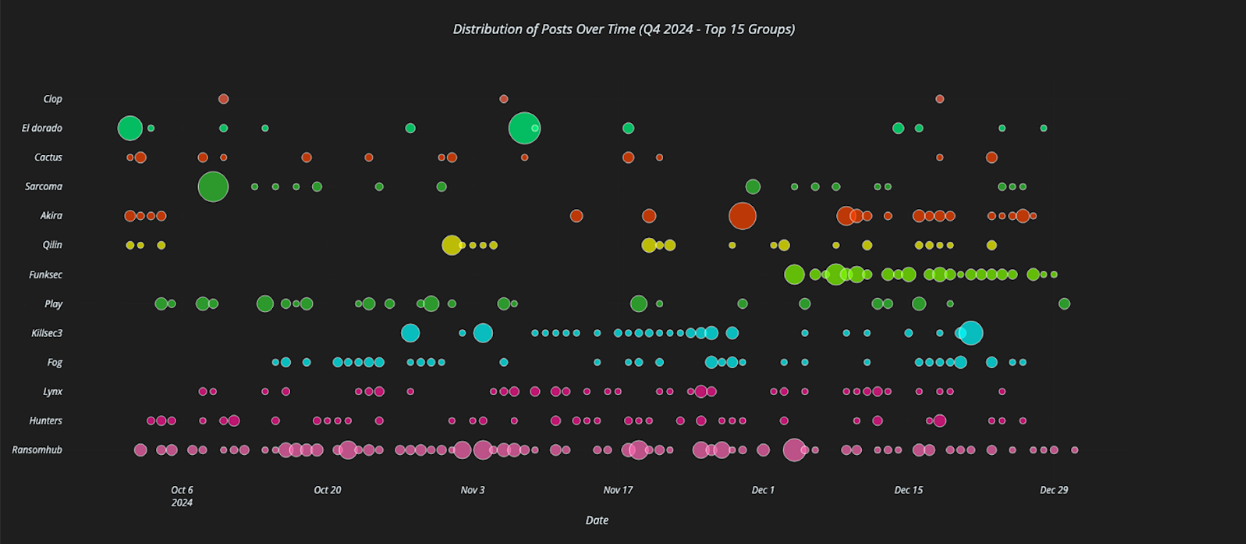
In the scatterplot below, we see Q4 2024 leak site post activity for the top 15 ransomware groups, where the dots indicate individual posts and the dot sizes indicate the amount of data being posted. Looking at Akira’s (5th from top) posting distribution, we can see that it is sporadic but its pace begins to increase around mid December. By way of comparison, RansomHub’s (bottom line) posting distribution is consistent and strong throughout the quarter.
2025 Ransomware: Business as Usual, Business is Booming

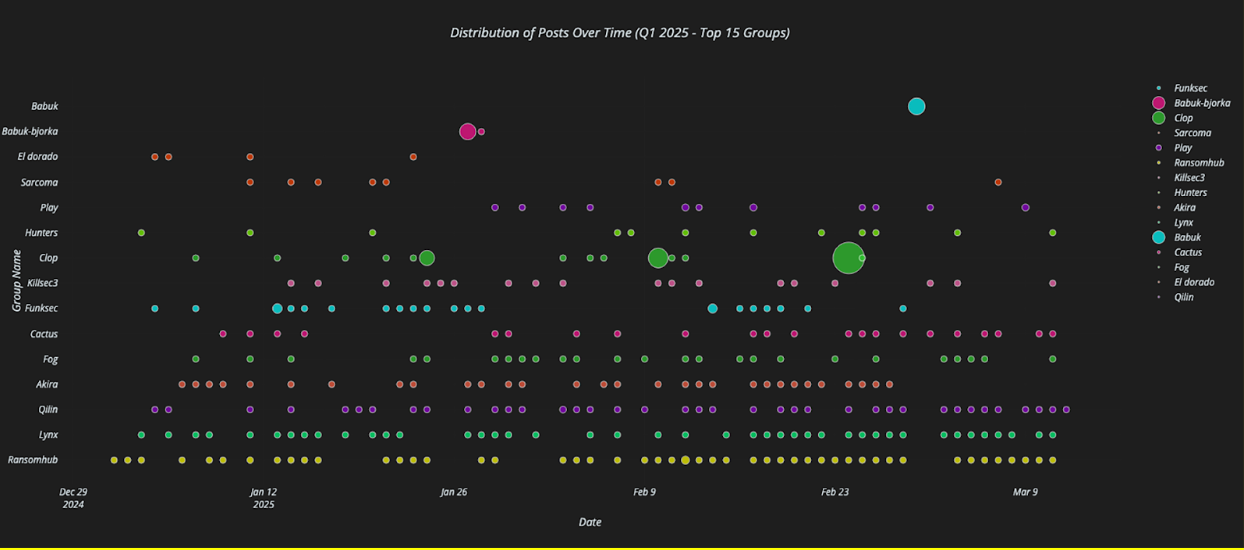
In the following scatterplot, which is Q1 2025, we see Akira (4th from bottom) operating much more in line with other leading players (Qilin, Lynx, etc.). Rather than sporadic, often large data dumps, Akira has begun to make regular postings of similar size. Further trends analysis shows that Akira’s postings shifted from happening primarily on Fridays to being anytime throughout the week.
2025 Ransomware: Business as Usual, Business is Booming

Ones to watch

As noted above, the most prolific ransomware groups for Q1 2025, ranked by the number of posts on their dedicated leak sites, are Cl0p and RansomHub by a considerable margin. Along with these two groups, several others are disrupting businesses of varying sizes and industries. In this section we’ll discuss groups of particular concern due to their reach and/or negative organizational impacts.

RansomHub

RansomHub burst onto the scene in February 2024, combining data encryption and exfiltration from a minimum of 210 organizations across a 6-month period. Affiliates are known to use vulnerability exploitation and phishing for initial access, along with double extortion to force victims into paying a ransom or face leaked data and reputational damage. RansomHub was the most prolific leak group operator we saw in 2024, and based on current trends displays no sign of slowing down.

Cl0p

Cl0p is one of the most well known Ransomware-as-a-Service (RaaS) groups. First seen in 2019, Cl0p has a long history of using exploits to propagate ransomware and leans heavily into double extortion. Cl0p is also known for its involvement in devastating supply-chain incidents, most notably claiming to have stolen data from hundreds of MOVEit Transfer customers. Initial access vectors include phishing emails, social engineering, and malicious attachments.

The group has made a torrent of leak site posts since the start of the year, with an astonishing 345 leak site posts in February alone and 413 for Q1 overall. While some of these posts represent fresh attacks, the majority are drip-fed leaks related to their exploitation of an older vulnerability in Cleo’s file transfer software.

Anubis

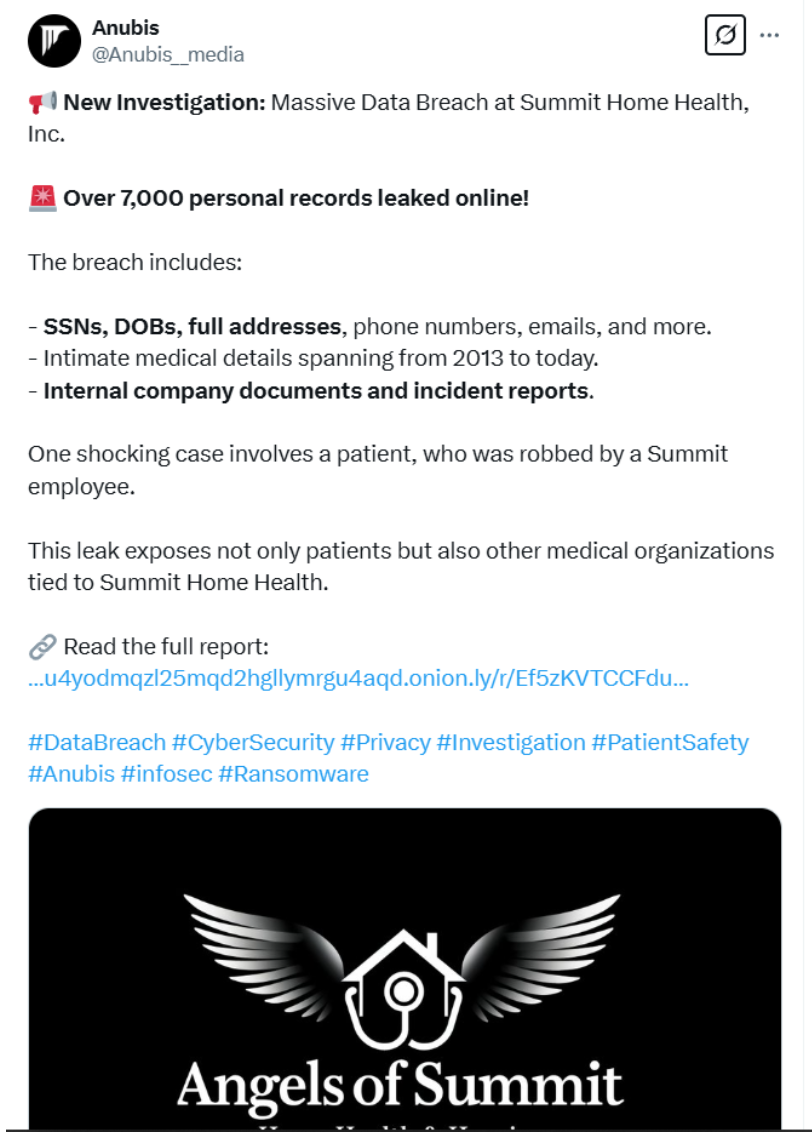
A new RaaS group active since at least November 2024 with a strong focus on data extortion, Anubis has possibly redefined the double extortion approach into something best described as malevolence as a service. It’s not enough to exfiltrate and then leak victim data; Anubis presents findings in a format resembling citizen journalism, exposing the alleged wrongdoings of those they target. The Robin Hood approach, hoping to curry favor with the public, is a well-worn one.

All of this, wrapped up in a slick format of nice graphics and hype-generating announcements on social media.
2025 Ransomware: Business as Usual, Business is Booming

It feels more like buying into membership of an airline loyalty program, as opposed to some kind of ruthless extortion. Already well into the “Watch out for our next exciting leak” promotional activity stage, this is a group making waves and has claimed at least five public victims so far, mainly in the healthcare and engineering sectors. Of note is that Anubis itself has stated it is looking to exclude education, government and non-profit sectors from its list of potential targets. Thus far, targeted regions appear to be the U.S., Canada, Europe, and Australia.

Lynx

First observed in July 2024, this now-established RaaS group combines phishing and malicious downloads alongside double extortion tactics. Lynx targets a variety of sectors including utilities, construction, and manufacturing, with victims located in a wide variety of locations including the U.S., Australia, and Romania.

Lynx offers a slick and professional affiliate panel, allowing affiliates to micromanage almost all aspects of a campaign and its unfortunate targets. The panel includes victim profile pages, news and updates, and an “all-in-one” archive of executables targeting multiple architectures. It’s the kind of setup which lowers the bar to entry for newcomers, and only becomes more popular over time.

Qilin

Although not as visible as some other ransomware groups in Q1 2025, RaaS operator Qilin has achieved some notable success. First observed in 2022, Qilin ransomware has been used to target a wide variety of industries which includes the healthcare, financial, and manufacturing sectors. Known for spear phishing and making use of compromised credentials, Qilin attacks tend to specialize in double extortion and data exfiltration on a large scale—their leaks can range from a few hundred gigabytes to their most recently publicized attack, which is allegedly a haul of 1.1 terabytes of data. Alarmingly, Microsoft has observed North Korean group Moonstone Sleet deploying Qilin ransomware at “a limited number of organizations”, the first time this group has been known to make use of ransomware developed by a RaaS threat actor.

Tactics

Ransomware groups tend to follow a specific pattern: Initial access, reconnaissance, credential theft and lateral movement, exfiltration, and finally encryption. There are divergences, however. Some groups avoid ransomware deployment and file encryption, instead choosing to compromise the network via unsecured VPNs and Remote Desktop Protocol (RDP). From there, they move straight to data exfiltration. This is known as “extortionware.”

Other threat actors, notably LockBit, use Living off the Land (LOTL) tactics to infiltrate networks with legitimate tools and management software already in place. As no malware files are deployed, it becomes increasingly difficult to detect these attacks in motion and threat actors can sit undetected for weeks or even months.

Here are some of the key elements of ransomware tactics across this first quarter of 2025:

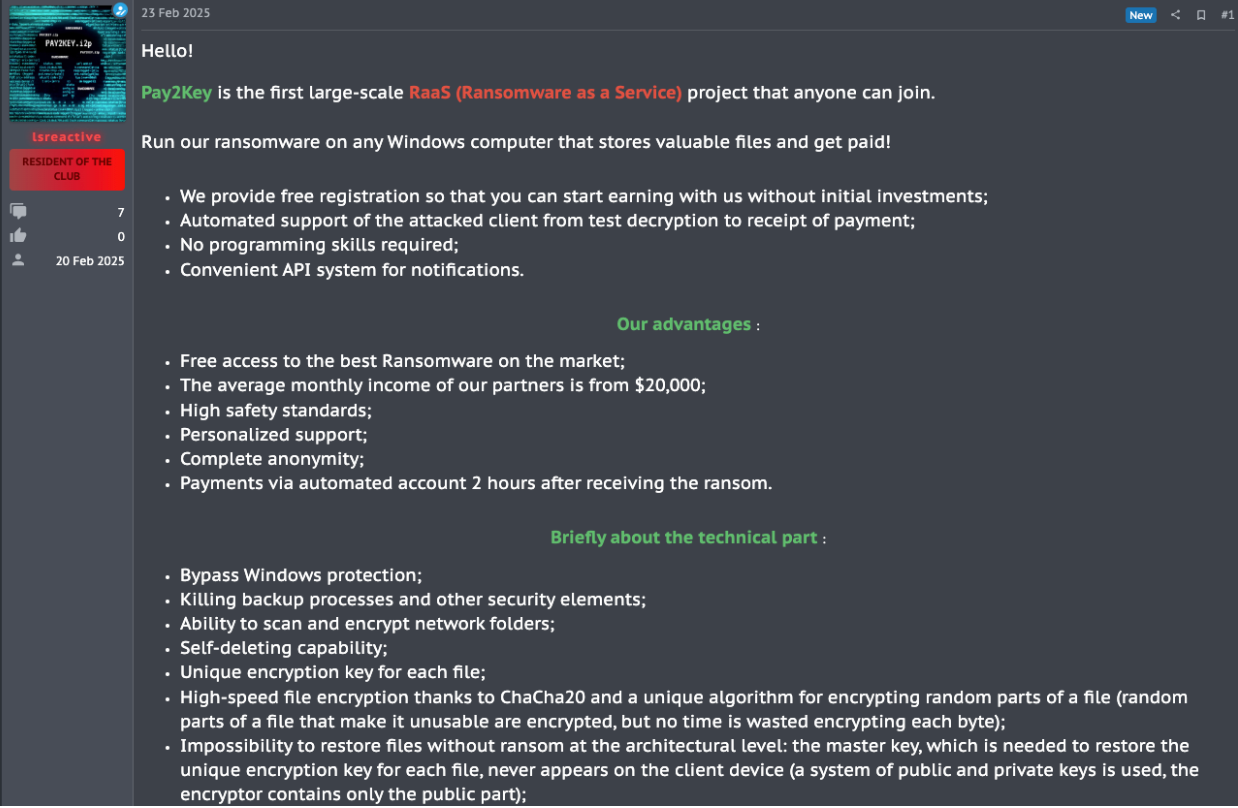
  • RaaS is firmly established as a key tactic for prominent ransomware groups. The ease with which affiliates can buy into a ransomware group of choice and immediately begin attacks (see example below) ensures a steady flow of profit for the criminals at the top of the food chain.
2025 Ransomware: Business as Usual, Business is Booming
  • Double extortion is also a firm favorite. FunkSec made inroads into this realm with ransoms as low as $10,000, perhaps designed to be more enticing to victims than the often unreachable demands for totals ranging from $600,000 to a cool million plus.
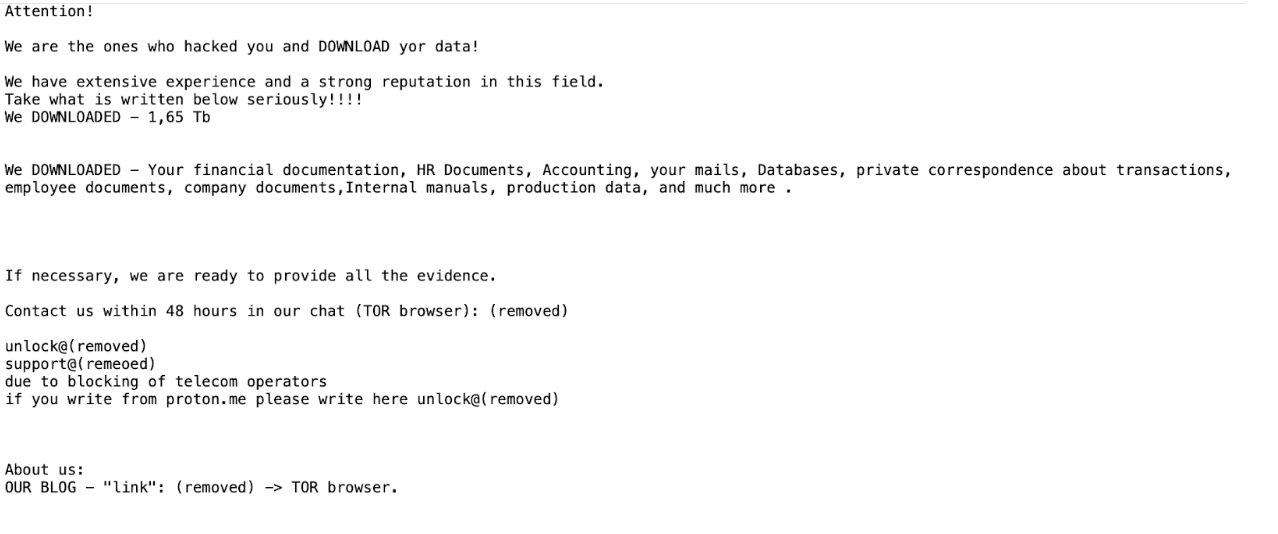
  • The deadline to pay a ransom, or just make initial contact with the threat actor, varies greatly between groups. RansomHub has previously handed out ransoms with deadlines ranging between 72 hours and 90 days. Cl0p has been known to apply varying degrees of pressure to encourage targets to get in touch. In December 2024, the group gave uncommunicative victims 48 hours to make contact or risk having their organization’s names disclosed publicly. Other Cl0p notes, such as the one below, reuse the 48-hour tactic but exclude mention of public exposure. Regardless of the tactics used, there’s no guarantee files will be unencrypted or stolen documents deleted from leak sites should the victims pay up. These supposed deadlines create a sense of urgency while potentially offering victims little beyond false hope.
2025 Ransomware: Business as Usual, Business is Booming

Five things you can do now

Unfortunately, there is no escaping the business reality of ransomware; it is a pervasive problem and it impacts every business at some level sooner or later. A solid defense plan can help to lower risk and prevent a disastrous outcome.

Here are five things you can do now that will make an immediate impact on reducing your attack surface:

  1. Take a fresh look at your MFA — If your organization has deployed multi-factor authentication (MFA), take the time now to review any policy exceptions that have been made over time and remove as many as possible. In addition, ensure that your MFA settings are properly configured (this is critical!). If your organization has not yet deployed MFA, see number 2.
  2. Deploy and configure MFA the right way — Multi-factor authentication is a must to avoid giving attackers an easy win from unsecured VPNs and RDP. Combine with geolocational restrictions, strong, unique passwords, and number matching in MFA applications to help ward off additional threats like MFA fatigue.
  3. Practice continuous patch management, especially for edge devices — Over the last couple of years, network edge devices have become a favorite way for attackers to gain initial access and then pivot elsewhere in the victim’s network. It’s critical that your patch management program accounts for this by prioritizing fixes to these devices as they are released. Prioritization of fixes should also be based on known exploits, their potential impacts to your business, and how these align with your business’s risk tolerance.
  4. Hold a ransomware attack simulation — Activate your incident response plan as if the organization has just been made aware of a breach. Who in the organization is involved and what are their immediate tasks? Are payment policies and outside resources pre-determined so there are no panic-driven mistakes and critical time isn’t lost? Note your learnings and schedule regular simulations every 6 months thereafter.
  5. Investigate your attack surface — Threat actors and their tools are poking and prodding your attack surface in search of vulnerabilities, and you must be proactive in doing the same. Resolve to speak with us regularly about Rapid7’s latest innovations in attack surface management.

Conclusion

Ransomware groups large and small have ushered in 2025 with a clear statement of intent: business as usual, and business is booming. The significant volume of leak posts and the heavy lean toward double extortion would indicate we can expect more of the same as the year progresses. In addition, the first glimmer of reportage-style commentary on their victim’s alleged failings suggests a bumpy road ahead for organizations unlucky enough to end up in the ransomware spotlight.

Newer groups hungry for publicity and affiliate network building will potentially look to emulate the Anubis approach, and do a little reportage style journalism of their own. Gimmicks sell and grab publicity, and reputational damage from data leaks may well go hand in hand with regulatory embarrassment and bad publicity. If that wasn’t bad enough, ransomware groups stand revealed through exposed chat logs as being in the market for purchasing zero days.

Businesses need to do everything they can to minimize the risk of easy network access and data exfiltration. Victims continue to pay the price for poor MFA coverage and inadequate patch management, which is why we heavily stressed these basics in our recommendations section above.

If there is a brave new world of ransomware to speak of, it largely resembles the old one with a few streamlined tweaks to a very well-oiled machine.
A Rebirth of a Cursed Existence? – The Babuk Locker 2.0

Post Syndicated from Rapid7 original https://blog.rapid7.com/2025/04/02/a-rebirth-of-a-cursed-existence-the-babuk-locker-2-0/

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0

Co-authored by Yaniv Allender and Anna Sirokova

A Rebirth of a Cursed Existence? Examining ‘Babuk Locker 2.0’ Ransomware

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0

Introduction

Ransomware remains a major threat, causing significant disruption and financial losses to organizations across various sectors. Cybercriminal groups behind these attacks constantly adapt their methods to maximize damage and profit.

At Rapid7, we actively monitor new cyber threats, keeping an eye on ransomware groups and their changing tactics. In early 2025, we came across a channel promoting itself as Babuk Locker. Since the original group had shut down in 2021, we decided to investigate whether this was a rebrand or a new threat. Several underground forums and Telegram channels started mentioning ‘Babuk Locker 2.0,’ with some actors taking credit for recent attacks. Since Babuk’s leaked source code in 2021 had led to many spin-off ransomware strains, we wanted to find out whether this was a real comeback or just another group using Babuk’s name.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
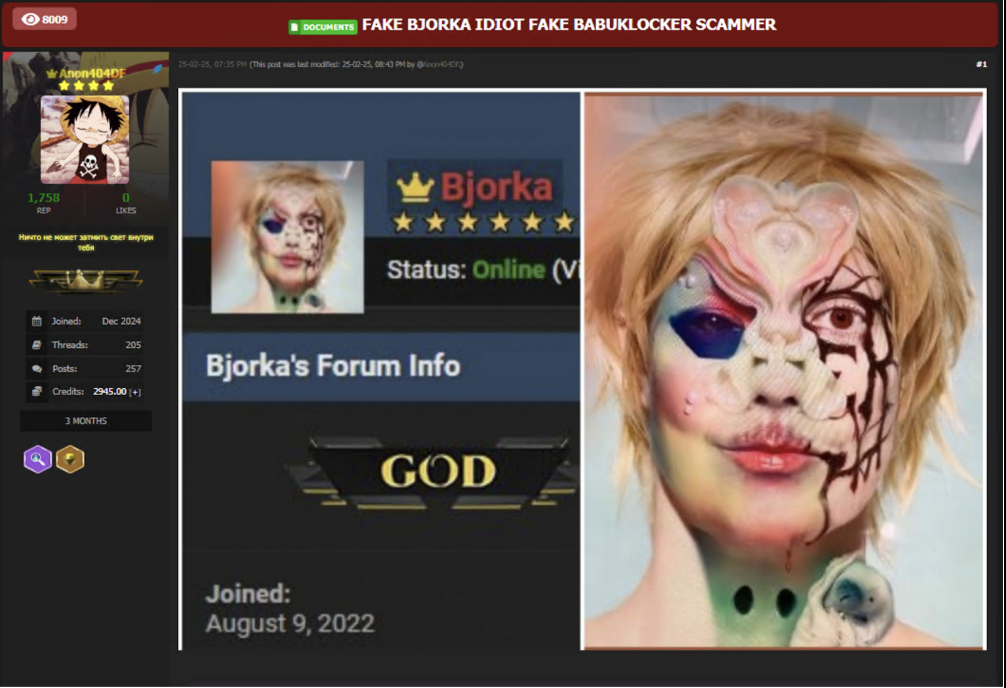
Figure 1 – Online discourse against Bjorka as a scammer
A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
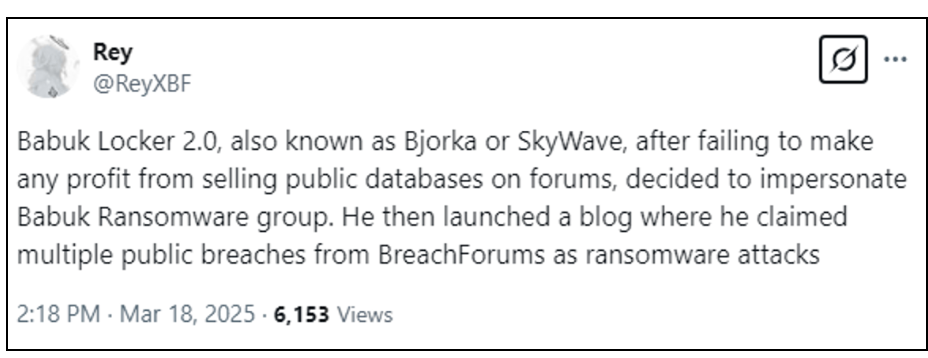
Figure 2 – Online discourse against Bjorka and SkyWave as scammers

We started by gathering intelligence from dark web marketplaces, hacker forums, and private Telegram groups. We saw a rise in discussions about Babuk’s return, often linked to two groups, ‘Skywave’ and ‘Bjorka.’ These actors claimed responsibility for major attacks, and their leak sites suggested they might be working with other cybercriminal groups.

This blog delves into the potential revival of Babuk Locker 2.0, its alleged operators, and their activities. We analyze the involvement of ‘Skywave’ and ‘Bjorka,’ their claimed victims, and the evolution of Babuk’s Ransomware-as-a-Service (RaaS) model. Our findings include technical analysis, victimology, and the broader risks posed by this campaign.

Operators: Skywave and Bjorka

While monitoring Babuk Locker 2.0 activity, we identified two key groups linked to its operations—Skywave and Bjorka. These groups frequently appeared in discussions on underground forums and Telegram channels, claiming responsibility for attacks and promoting Babuk-related leaks. Our analysis suggests that these groups play a significant role in Babuk Locker 2.0’s activities, either as affiliates or key operators.

Skywave

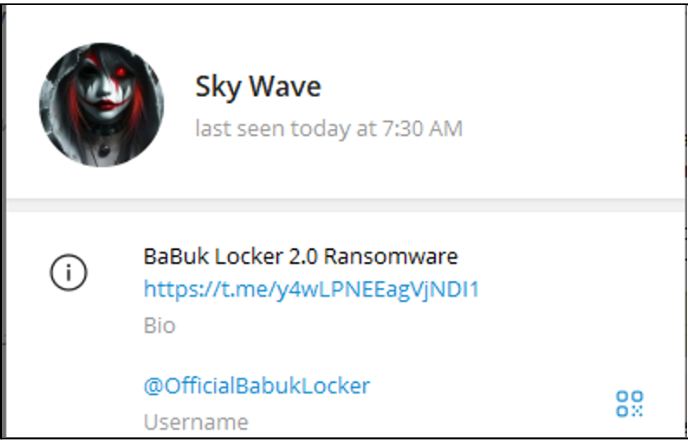
Skywave is a recently identified threat actor known for allegedly executing cyberattacks against various high-profile organizations and government agencies. Their operations have raised concerns within the cybersecurity community due to the sensitivity and volume of the data reportedly compromised, as well as the anonymity of the operator. Skywave is suspected of operating multiple Telegram channels under different aliases, some of which have been flagged as scams and removed by Telegram.

The specific TTPs employed by Skywave remain undisclosed, leaving room for speculation regarding their infiltration and data exfiltration methods. Since late 2024, Skywave has maintained its presence on various platforms, such as Telegram, DarkForums, and the dedicated Babuk Locker 2.0 DLS, where they have been sharing leaked data from their allegedly recent attacks. Victim lists indicate a focus on high-profile organizations with sensitive data.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 3 – The Telegram user of Skywave

Bjorka

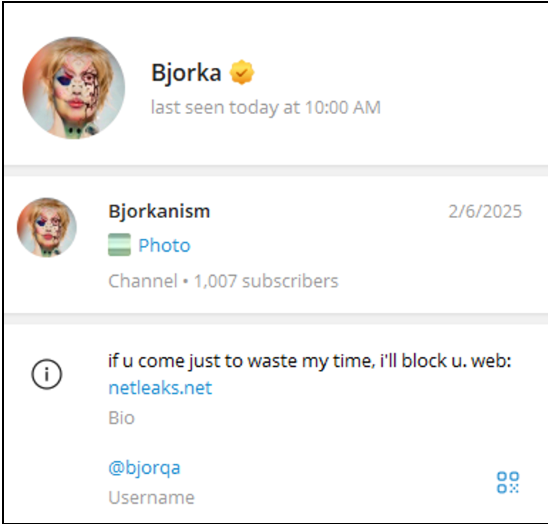
Bjorka is a threat actor mainly known for allegedly breaching Indonesian government and citizen data, often leaking sensitive information as a form of hacktivism. The alias gained prominence in 2022 with a series of high-profile data leaks, first making headlines in March by exposing over 105 million Indonesian voter records. Throughout 2022, Bjorka targeted multiple institutions, leaking personal data to highlight security flaws and criticize policies. By August 2022, Bjorka joined BreachForums, where they are sharing large databases from breached telecom services. Authorities attempted to identify the hacker, even arresting an individual, but Bjorka mocked the effort, claiming the wrong person was caught. The threat actor is active on BreachForums and Telegram and owns a personal leak site (netleaks[.]net) to distribute stolen data and engage followers.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 4 – The Telegram user of Bjorka

Babuk Locker 2.0/Babuk-Bjorka

Since February 2025, Skywave has claimed ownership on at least 5 different Telegram channels and posts daily about their previous and current victims. Throughout the research, we found dozens of newly created Telegram channels with the names ‘Babuk Locker 2.0’, ‘Babuk 2.0 Ransomware Affiliates’, etc. Some of which overlapped with one another. Additionally, several channels were labeled as scams by Telegram itself and were unavailable a couple of days after they were created.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 5 – A Babuk Locker Telegram channel labeled as a scam by the platform

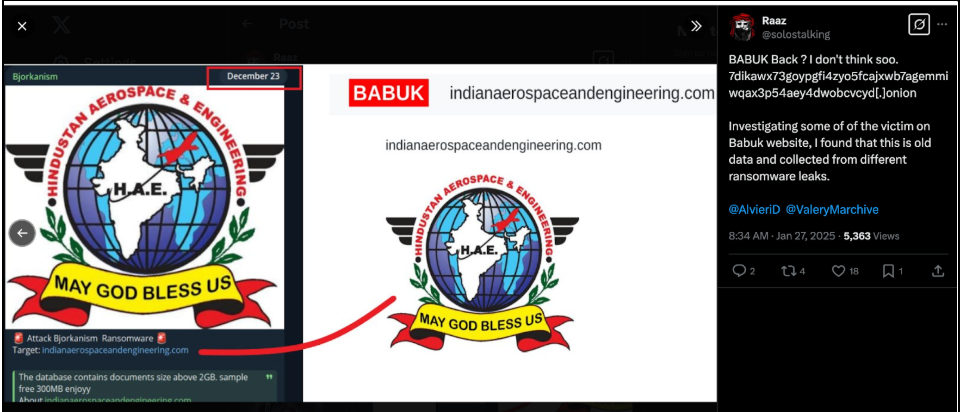
During our research, we noticed the consistent amplification of the Babuk 2.0 content by Bjorka on their Telegram channel. Speculation about the possible affiliation between Babuk and Bjorka rose due to the overlap of victims, such as the case of ‘Hindustan Aerospace & Engineering’ from India. The organization was initially reported as a victim of Bjorka in December 2023, and again as a victim of Babuk as of March 2025.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 6 – Overlap of victimology between Bjorka and Babuk 2.0

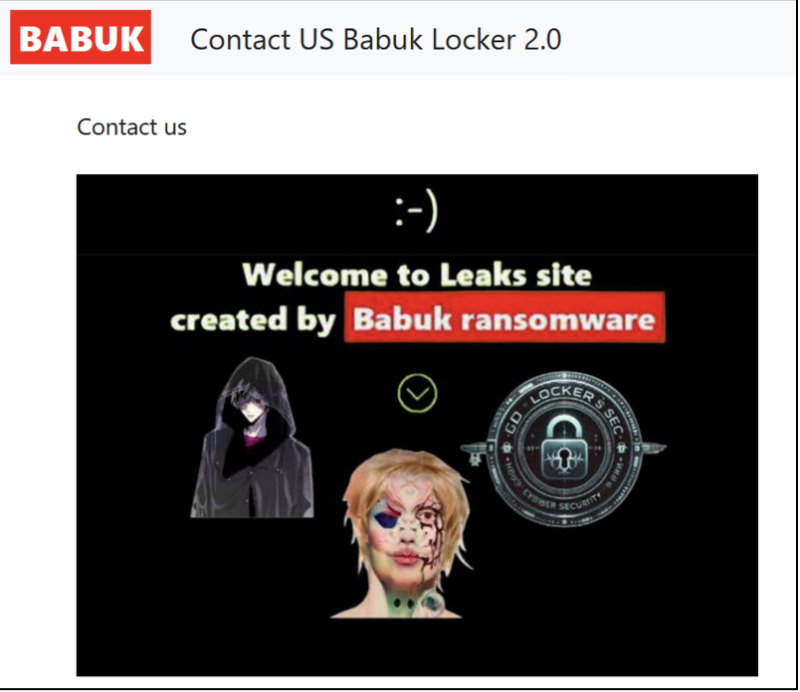
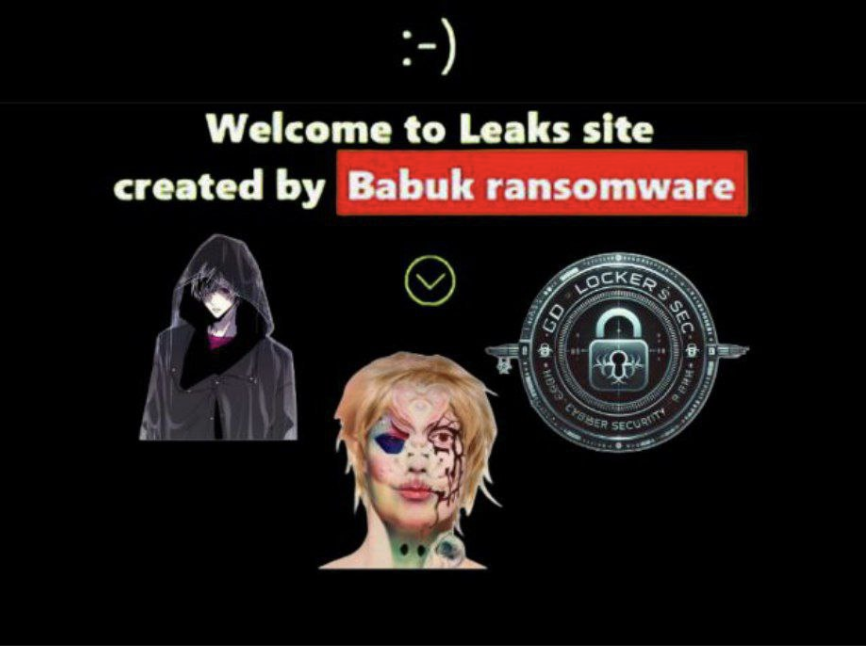
Further evidence of a possible collaboration between the threat actors emerges from the ‘Contact Us’ tab on Babuk’s DLS, where the logos of Skywave and Bjorka appear next to each other, as well as another possible affiliate named GD Locker Sec.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 7 – The ‘Contact US’ tab on the DLS of Babuk, showing the logos of Bjorka and Skywave

Technical Analysis

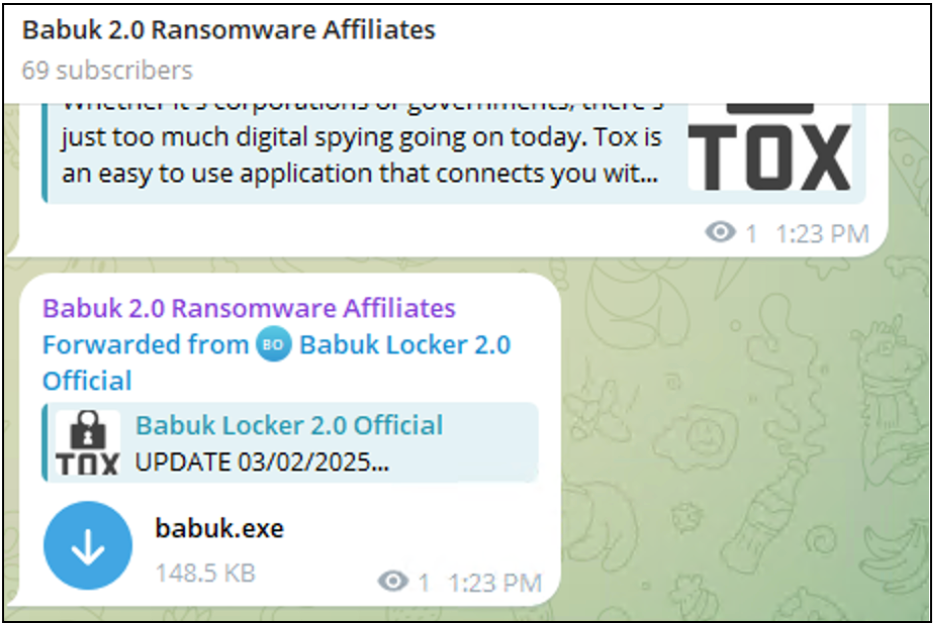
A sample named babuk.exe SHA-256 3facc153ed82a72695ee2718084db91f85e2560407899e1c7f6938fd4ea011e9 was initially shared on the Telegram channel “Babuk 2.0 Ransomware Affiliates”, before being forwarded to another operational account. Upon analysis, it turned out not to be Babuk Locker at all, but rather LockBit 3.0 also known as LockBit Black. This case is yet another example of the well-established trend: threat actors rebranding ransomware strains, whether to confuse researchers, lure affiliates, or just keep the marketing fresh. Either way, babuk.exe is just LockBit 3.0/Black wearing a fake name.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 8 – “Babuk” sample shared on Babuk 2.0 Affiliate Group Telegram channel

LockBit 3.0 Overview

LockBit 3.0/Black, is a ransomware variant that shares similarities with BlackMatter ransomware. On September 21, 2022, a user named @ali_qushji leaked the LockBit 3.0 builder on Twitter. The leak code made it easy for the least skilled attackers to join the game.

Encryption Methods

An analyzed sample of LockBit 3.0 uses a combination of AES-256 and RSA-2048 encryption. AES-256 is used to encrypt victim files and RSA-2048 encryption used to encrypt the AES key, ensuring decryption is impossible without the attacker’s private key.

Terminated Processes and services

LockBit 3.0 terminates various applications and system processes (the full list is in the table below) most likely to maximize encryption efficiency and prevent file access conflicts. It also disables key security and backup services to limit recovery possibilities and increase impact.

Terminated Processes Terminated Services
sql vss
oracle sql
ocssd svc
dbsnmp memtas
synctime mepocs
agntsvc msexchange
isqlplussvc sophos
xfssvccon veeam
mydesktopservice backup
ocautoupds GxVss
encsvc GxBlr
firefox GxFWD
tbirdconfig GxCVD
mydesktopqos GxCIMgr
ocomm
dbeng50
sqbcoreservice
excel
infopath
msaccess
mspu
onenote
outlook
powerpnt
steam
thebat
thunderbird
visio
winword
wordpad
notepad
calc
wuauclt
onedrive

Active Directory Enumeration

LockBit 3.0 uses logoncli_DsGetDcNameW API function used for Active Directory (AD) enumeration. To brute-force AD accounts, analyzed LockBit 3.0 sample came preloaded with Base64-encoded username and password combinations decoded and listed below.

Username Password
bad.lab Qwerty
Administrator 123QWEqwe
@#Admin2 P@ssw0rd
Administrator P@ssw0rd
Administrator Qwerty
Administrator 123QWEqwe
Administrator 123QWEqweqwe

Babuk or LockBit 3.0? Rebranding Won’t Change the Code.

Analysis confirms that babuk.exe, advertised in the Babuk 2.0 Ransomware Affiliates Telegram channel, is actually based entirely on LockBit 3.0 source code—not Babuk. The sample shows key techniques identical to previous LockBit 3.0 variants, reinforcing that this is yet another case of threat actors rebranding existing ransomware rather than introducing anything genuinely new.

Key Overlapping Techniques

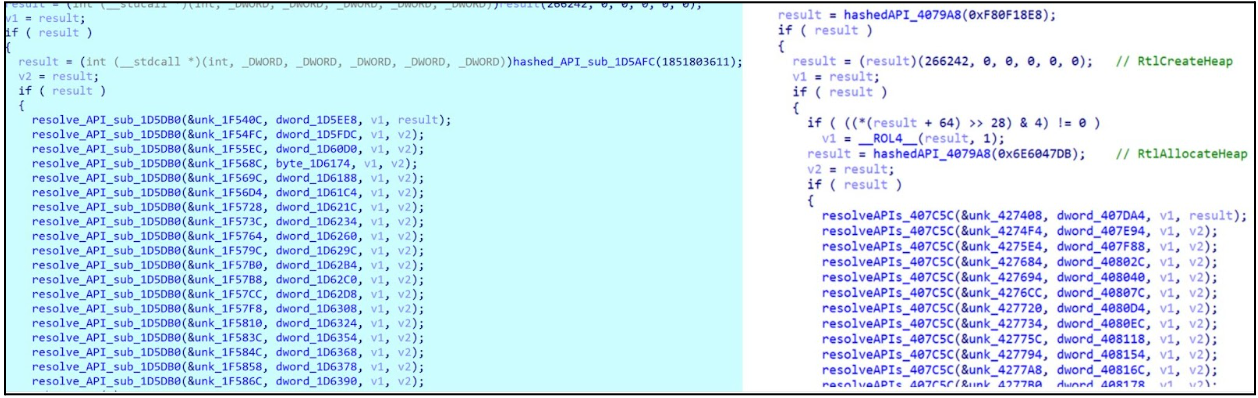
The analyzed sample uses API harvesting by hashing API names from DLLs and comparing them against a predefined list of required APIs (Figure 7). This technique, likely to obfuscate API calls and evade detection, mirrors the approach seen in Lockbit3.0/Black and aligns with previous findings by Trend Micro.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 9 – LockBit 3.0’s routine for API harvesting function comparison—our analyzed sample (left) vs. TrendMicro’s reported sample (right).

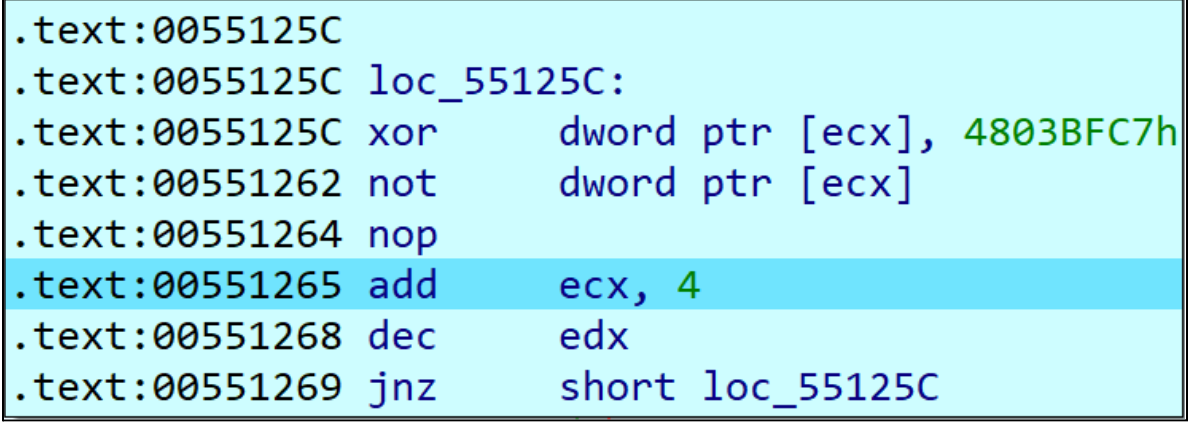
Likewise, The XOR key 0x4803BFC7 LockBit 3.0 used for renaming APIs is the same as it was reported before. The xor key is re-used multiple times in the code.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 10 – 0x4803BFC7 xor key observed in analyzed sample

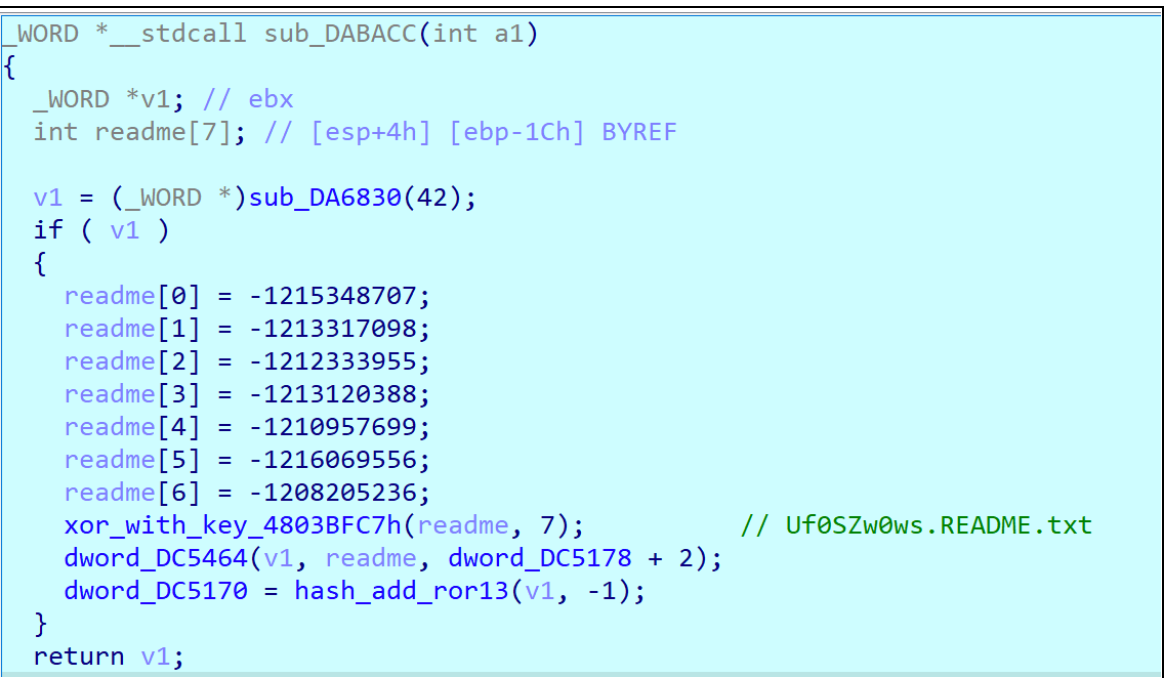
Additionally, the ransom note creating routine is identical as in previous Lockbit3.0/Black samples.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 11 – readme creation routine

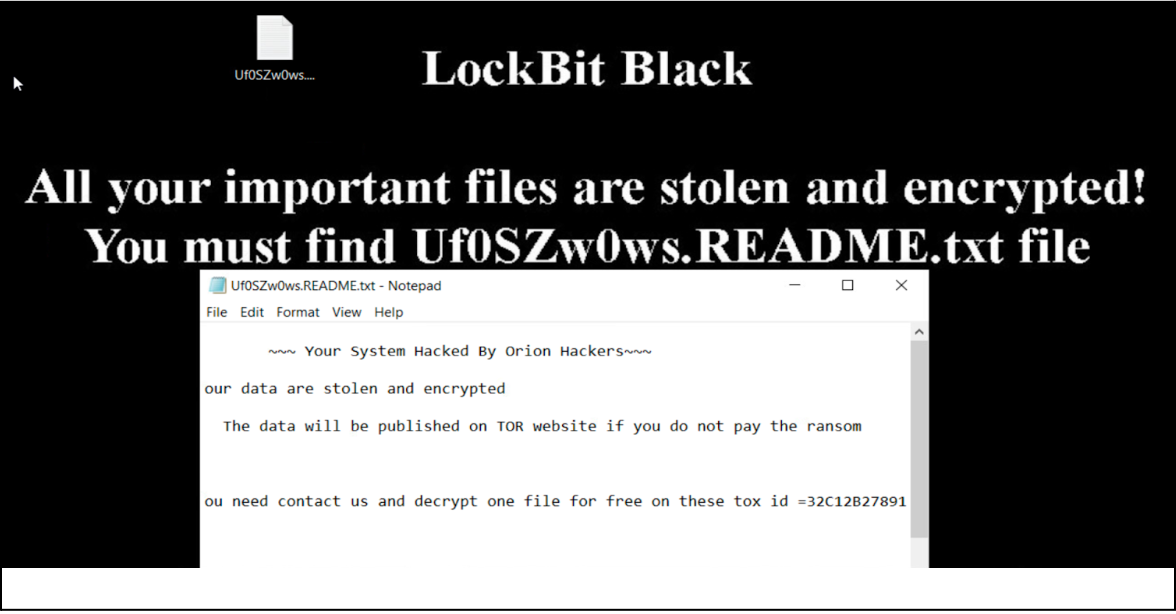
Like previous LockBit 3.0/ Black samples, the analyzed variant modifies the desktop wallpaper to display a ransom note—branded, unsurprisingly, as “LockBit Black” (not Babuk, in case anyone was still confused). It also appends specific extensions to encrypted files, changes their icons, and drops a .ico file in the %PROGRAMDATA% directory, staying true to the LockBit playbook.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 12 – Lockbit3.0 wallpaper and ransom note

The ransom note referenced “Orion Hackers” and the tox ID 32C12B278912E26E5EAC57AEBB3F4FF16F0E31603C7B9D46AC02E9D993EE14351CEC3AB5945C. A search on this TOX ID linked the ransom demands to the `Babuk 2.0 Affiliate Group` on Telegram. Additionally, we discovered that messages from this channel were being reposted by an actor named Bjorkanism, who is actively sharing content from Affiliate Group Babuk 2.0 which is actually leaked Lockbit3.0.

Victimology

The new Babuk Locker 2.0 has recently been making waves within the cybersecurity and intelligence scene, claiming dozens of high-profile cyberattacks in a short time of less than two months of operation. Since January 2025, the group has listed at least 100 organizations as their alleged victims. Among their alleged victims are Amazon, the Israeli Knesset, Sodexo, and other high-profile organizations. Victims are from multiple sectors including energy, manufacturing, IT, government, etc.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 13 – Victims listed on the Babuk Locker 2.0 DLS
A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
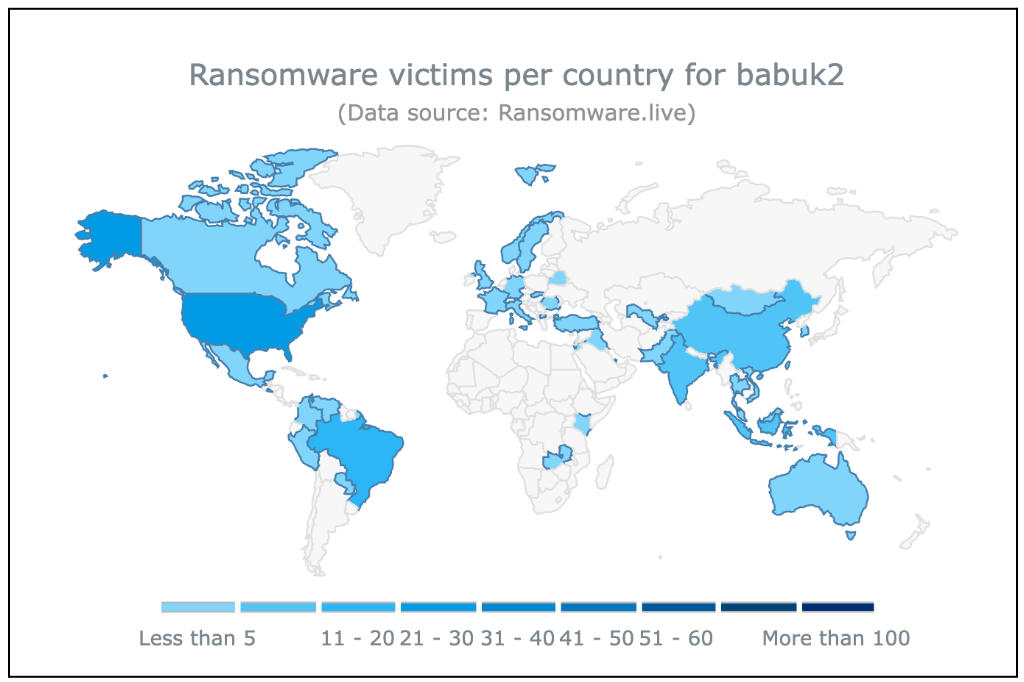
Figure 14 – Babuk Locker 2.0 victims per country

There have been growing claims of overlaps between Babuk Locker 2.0 and other ransomware groups, as some of their alleged victims were already attacked by other groups, such as HellCat, RansomHub, FunkSec, and others. These overlaps in victimology reinforce concerns about the authenticity of the new Babuk group entity and its operations.

A Rebirth of a Cursed Existence? - The Babuk Locker 2.0
Figure 15 – Babuk Locker 2.0 victims overlap with another ransomware group

Conclusion

Babuk Locker 2.0 is not a true revival of the original Babuk group—it’s just LockBit 3.0 with a new label. Our analysis strongly suggests that Skywave and Bjorka are behind this operation, either as collaborators or opportunistic actors riding the same wave.

Despite its bold claims, Babuk 2.0’s victim list overlaps heavily with other ransomware groups, raising doubts about the legitimacy of its attacks. Rather than a sophisticated new threat, this looks more like a rebranding stunt—a common tactic among ransomware operators to confuse defenders, attract affiliates, and inflate their reputation.

This case reinforces a familiar pattern: ransomware groups don’t disappear—they just change names, recycle code, and keep cashing in. Whether Skywave and Bjorka are working together or simply using Babuk’s name for credibility, one thing is clear: Babuk 2.0 is just LockBit 3.0 in a different costume.

IOCs (Indicators of Compromise)

DLS (Data Leak Sites)
7dikawx73goypgfi4zyo5fcajxwb7agemmiwqax3p54aey4dwobcvcyd.onion
imblth46g3x5oo444wkjn7umj4g26tnhmrlo53ovfqmmkmughdw4j2ad.onion
bxwu33iefqfc3rxigynn3ghvq4gdw3gxgxna5m4aa3o4vscdeeqhiqad.onion
Telegram Handles
@OfficialBabukLocker
@BabukLockerRaasSHA1
@BabukLockerRaas (inactive)
@BGLocker
Tox ID & Contact
Tox: 022A7EEB83B648F55DA7A6BEFD130C2156C74F3501A31D853234EC2D18E77A1E5BEC7F60201
Email: [email protected]
YouTube: youtube.com/@babuklocker
Ransomware samples obtained from Telegram channels
3facc153ed82a72695ee2718084db91f85e2560407899e1c7f6938fd4ea011e9
bdc482583a330a4682d13bfb7a0cf75b2fa350ac536064bce7b2bdd9d875de4a
0192eaf2ea5a52fa9d2398b3a2f69c163d47b368cd131ccae60df0a98c1fa2ca

Fake BianLian Ransomware Letters in Circulation

Post Syndicated from Chris Boyd original https://blog.rapid7.com/2025/03/19/fake-bianlian-ransomware-letters-in-circulation/

At a glance:

  • The FBI is warning of a mail-based fraud involving letters sent to businesses in the U.S. These letters resemble online ransomware notes demanding payment via Bitcoin.
  • Rapid7 examined a mail-based ransom demand sent to a customer from a local postcode.
  • There is no evidence that any of the recipients have been compromised by BianLian.

From BianLian: “Time Sensitive, Read Immediately”

Fake BianLian Ransomware Letters in Circulation

On March 5, the FBI issued an alert regarding a mail scam targeting U.S. business executives with extortion. The letters claim to be from noted ransomware group BianLian, demanding a payment in Bitcoin ranging from $250,000 to $500,000 within ten days of receipt.

The FBI alert reads as follows:

“Stamped “Time Sensitive Read Immediately”, the letter claims the “BianLian Group” gained access into the organization’s network and stole thousands of sensitive data files. The letter then goes on to threaten that the victim’s data will be published to BianLian’s data leak sites if recipients do not use an included QR code linked to a Bitcoin wallet to pay between $250,000 and $500,000 within ten days from receipt of the letter, claiming the group will not negotiate further with victims.”

The ransom note also warns recipients not to contact law enforcement, stressing that the FBI “does not care” about victims and will not help in the event of a lawsuit — a classic social engineering pressure tactic.

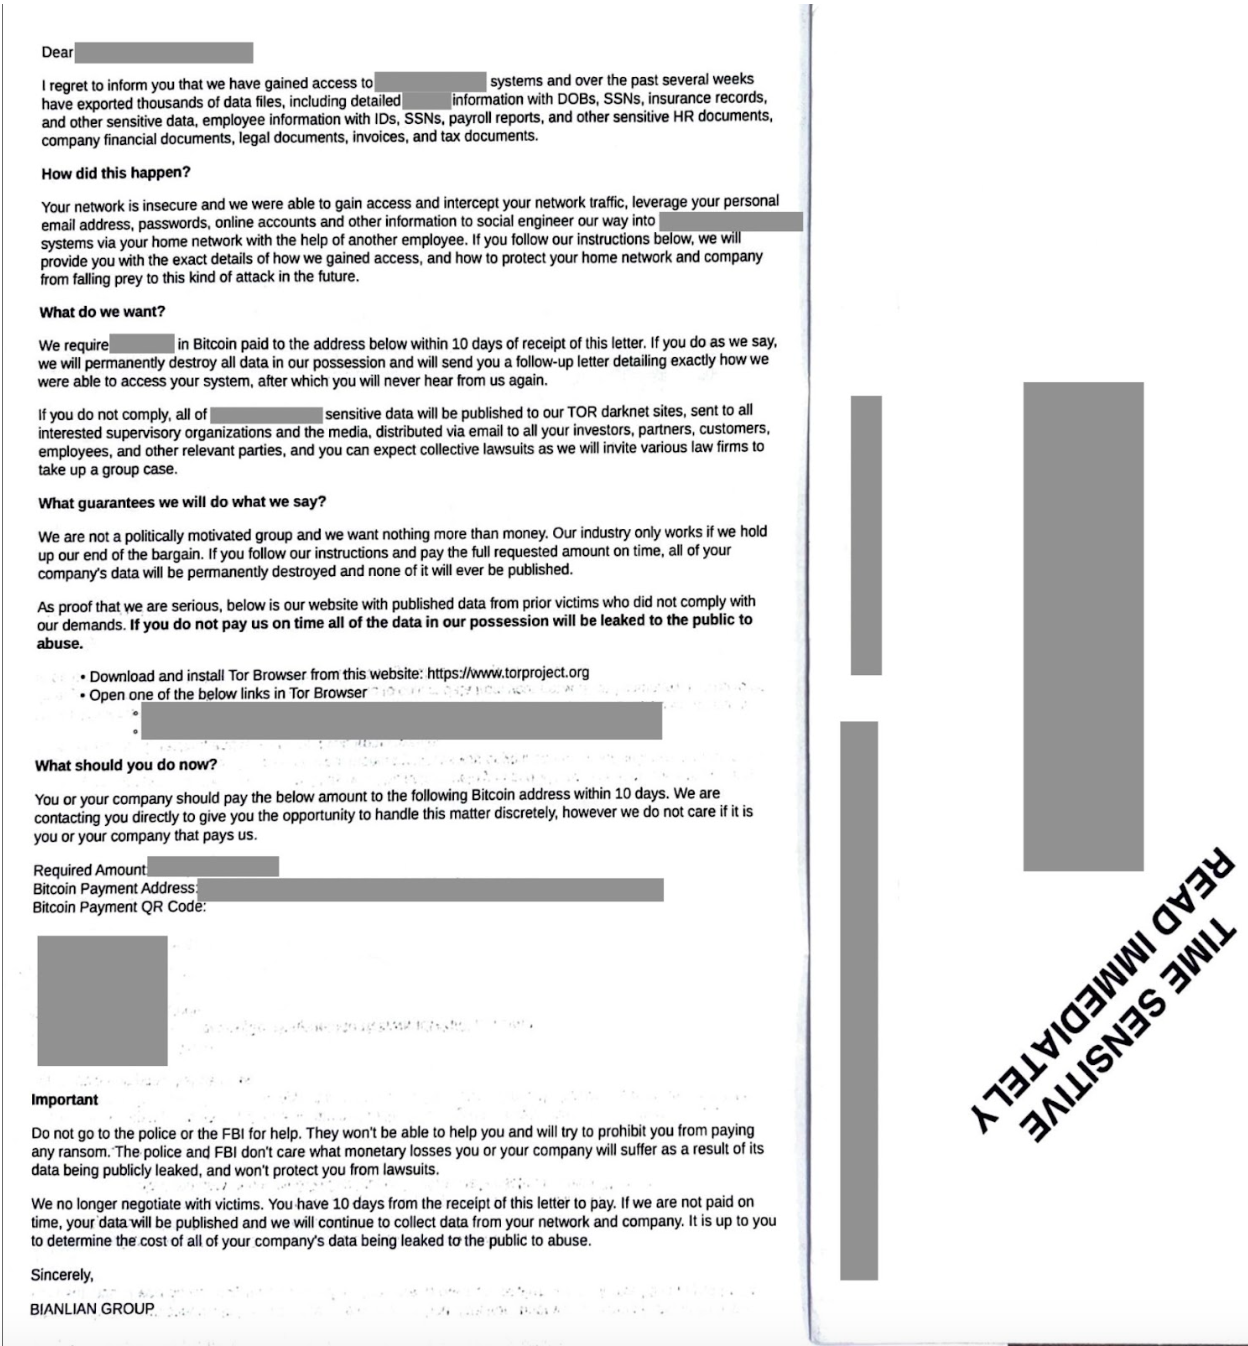
Rapid7 has observed that these letters are still in circulation, with one such letter received by a Rapid7 customer highlighted below. While we have redacted parts of the letter to protect the customer’s identity and other sensitive information, you can see that it follows the pattern of others seen in the wild, falsely claiming to be from BianLian:

Fake BianLian Ransomware Letters in Circulation

It reads:

“I regret to inform you that we have gained access to [redacted] systems and over the past several weeks have exported thousands of data files, including detailed [redacted] information with DOBs, SSNs, insurance records, and other sensitive data, employee information with IDs, SSNs, payroll reports, and other sensitive HR documents, company financial documents, legal documents, invoices, and tax documents.

How did this happen?

Your network is insecure and we were able to gain access and intercept your network traffic, leverage your personal email address, passwords, online accounts and other information to social engineer our way into [redacted] systems via your home network with the help of another employee. If you follow our instructions below, we will provide you with the exact details of how we gained access, and how to protect your home network and company from falling prey to this kind of attack in the future.

What do we want?

We require [redacted] in Bitcoin paid to the address below within 10 days of receipt of this letter. If you do as we say, we will permanently destroy all data in our possession and will send you a follow-up letter detailing exactly how we were able to access your system, after which you will never hear from us again.

If you do not comply, all of [redacted] sensitive data will be published to our TOR darknet sites, sent to all interested supervisory organizations and the media, distributed via email to all your investors, partners, customers, employees, and other relevant parties, and you can expect collective lawsuits as we will invite various law firms to take up a group case.”

The above letter is a match for those received by multiple businesses. Similarly, the Bitcoin payment address does not appear to be connected to the genuine BianLian group—just like several other examples highlighted online.
What you need to do

The FBI has issued the following advice, which is still applicable to this example of mail-based fraud:

  • Notify corporate executives and the organization of the scam for awareness.
  • Ensure employees are educated on what to do if they receive a ransom threat.
  • If you or your organization receive one of these letters, ensure your network defenses are up to date and that there are no active alerts regarding malicious activity.
  • If you discover you are a victim of BianLian ransomware, please visit [the FBI’s] Joint Cybersecurity Awareness Bulletin for recent tactics, techniques, and procedures and indicators of compromise to help organizations protect against ransomware.The FBI also requests that victims report any incident to their local FBI Field Office or the Internet Crime Complaint Center (IC3).

Additionally, Rapid7 recommends the following:

  • Do not scan any QR codes or go to any web links within the letter.
  • Do not pay any ransom.
  • Secure both the letter and envelope in a chain of custody evidence bag, or a ziplock if unavailable.

While ransomware actually was sent through the mail via infected USB sticks in 2022 by threat actor FIN7, that is not the case here. Recipients have not been compromised by BianLian despite what said letters claim. While your business is unlikely to receive one of these letters, other fraudsters may follow suit so a few moments spent warning of the dangers of this tactic may help to prevent an avoidable financial loss.

Disaster Recovery 101: Backup vs. Replication

Post Syndicated from Kari Rivas original https://www.backblaze.com/blog/disaster-recovery-101-backup-vs-replication/

A decorative image showing icons that represent file types being uploaded to the cloud.

I’ve heard the horror stories, and I’m sure you have too. A company thinks they’re covered because they have replication running, only to realize too late that replication doesn’t protect against data corruption or ransomware. In a disaster scenario, every copy of their critical data is compromised. And then comes the dreaded question: Do we have a backup?

Many teams—even those with seasoned IT professionals—misunderstand the fundamental difference between backup and replication for disaster recovery (DR). Replication is about availability, or keeping systems running with minimal downtime. Backup is about recoverability, or ensuring you can go back to a known good state.

This post breaks down replication, backup, and their respective roles in disaster recovery in a way that’s easy to share with your team, helping to prevent costly misunderstandings.

What is data replication?

Data replication involves copying and synchronizing data between your primary site and the DR destination in real-time or near real-time. It offers fast failover capabilities as the replicated data at the DR site is constantly updated. However, if malware infects your primary site, it might also replicate to the DR site, rendering the backup compromised.

What is data backup?

Data backup involves creating full and incremental copies of your data and storing them in a separate location from your primary system, typically on a scheduled basis, to prevent loss, corruption, or disasters. A couple key points:

  • Incremental backups capture changes in data, thus offering a point-in-time recovery option.
  • Ideally, backups are immutable, meaning they can’t be altered, in order to protect against malware and ransomware by making files and images read-only for safe recovery.
  • Air-gapped and offline backups can further help resist malware and ransomware attacks by creating a virtual or physical separation from the production network.
  • Cloud-based backups are a great option for addressing these requirements while offering affordable scaling options as the environment grows. 

Replicating backups

A hybrid approach involves replicating your backups to a secondary location, offering a balance between data protection and recovery time. This can be between on-premises and cloud environments, or across multiple cloud targets.

While replicating backups offers additional protection and accessibility for online recovery, the backup images are still subject to ransomware infection. Using immutable backups helps prevent the spread of the infection to recovery sites and backup repositories.

Data backups paired with replication can be an ideal strategy. Full and incremental backups with point-in-time snapshots can provide regular recovery points with replicated copies for remote recovery and additional protection. 

Cloud Replication

Backblaze B2 Cloud Replication enables your data to be automatically copied from one location to another for redundancy, compliance, and fast local access. Create 2x backups for a stronger disaster recovery posture. Replicating your Backblaze data is easy and free—no service or egress fees—just the standard Backblaze B2 Cloud Storage rates.

Learn More ➔ 

Disaster recovery and backups: Factors to consider when choosing the right approach

The optimal approach to disaster recovery backup and when and how you use replication depends on your specific needs.

  • For frequently accessed data requiring near-instantaneous recovery, consider a combination of a hot site methodology and real-time data replication. This offers the fastest failover, but can come at a higher cost.
  • For critical data with acceptable downtime, a warm site with replicated immutable backups at a secondary location (either on-premises or in the cloud) provides a good balance between cost and recovery time. While requiring some manual intervention, it offers protection against malware replicating to the DR site.
  • For less critical data or archival purposes, cold storage with periodic backups is a cost-effective option. Backups offer a historical record and are less susceptible to malware infection compared to replicated data, particularly if Object Lock is enabled for immutability.

Data replication is important, but it should not be seen as a substitute for backups. Backups offer a required safety net, providing a point-in-time recovery option even if the replicated data is compromised. Selecting the right disaster recovery backup strategy depends on a careful evaluation of your company’s specific needs, budget, and risk tolerance. 

By understanding the pros and cons of each option, you can make an informed decision that ensures optimal protection for your critical data in the face of unforeseen disruptions.

The post Disaster Recovery 101: Backup vs. Replication appeared first on Backblaze Blog | Cloud Storage & Cloud Backup

CISA Under Trump

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2025/01/cisa-under-trump.html

Jen Easterly is out as the Director of CISA. Read her final interview:

There’s a lot of unfinished business. We have made an impact through our ransomware vulnerability warning pilot and our pre-ransomware notification initiative, and I’m really proud of that, because we work on preventing somebody from having their worst day. But ransomware is still a problem. We have been laser-focused on PRC cyber actors. That will continue to be a huge problem. I’m really proud of where we are, but there’s much, much more work to be done. There are things that I think we can continue driving, that the next administration, I hope, will look at, because, frankly, cybersecurity is a national security issue.
If Project 2025 is a guide, the agency will be gutted under Trump:

“Project 2025’s recommendations—essentially because this one thing caused anger—is to just strip the agency of all of its support altogether,” he said. “And CISA’s functions go so far beyond its role in the information space in a way that would do real harm to election officials and leave them less prepared to tackle future challenges.”
In the DHS chapter of Project 2025, Cucinelli suggests gutting CISA almost entirely, moving its core responsibilities on critical infrastructure to the Department of Transportation. It’s a suggestion that Adav Noti, the executive director of the nonpartisan voting rights advocacy organization Campaign Legal Center, previously described to Democracy Docket as “absolutely bonkers.”

“It’s located at Homeland Security because the whole premise of the Department of Homeland Security is that it’s supposed to be the central resource for the protection of the nation,” Noti said. “And that the important functions shouldn’t be living out in siloed agencies.”

The 2024 Ransomware Landscape: Looking back on another painful year

Post Syndicated from Christiaan Beek original https://blog.rapid7.com/2025/01/27/the-2024-ransomware-landscape-looking-back-on-another-painful-year/

The 2024 Ransomware Landscape: Looking back on another painful year

The ransomware landscape in 2024 continued to evolve at a rapid pace, outgrowing many of the trends we saw in 2023. Threat actors remained relentless and innovative, targeting organizations of all sizes and sectors. In this post, we’ll examine the latest data points, discuss notable groups, and estimate the potential impact on victims — helping security teams plan their defenses for the months ahead.

2024 by the Numbers

Mid last year, Rapid7 Labs released our Ransomware Radar Report highlighting key stats for the first half of 2024. Here is how 2024 played out as a whole:

  • Total number of leak site posts: 5,939
  • Number of active ransomware groups: 75
  • Average number of active groups per month: 45
  • Average ransom payment in Q3 2024: $479,237 (Source: Coveware)
  • Median ransom payment in Q3 2024: $200,000 (Source: Coveware)
  • Median percentage of companies that pay: 32% (Source: Coveware)

These numbers offer insight into just how expansive ransomware activity has become. While the overall figures are alarming, it’s the variety of actors and their ability to adapt that pose the greatest challenge for defenders.

Top 10 Ransomware Groups

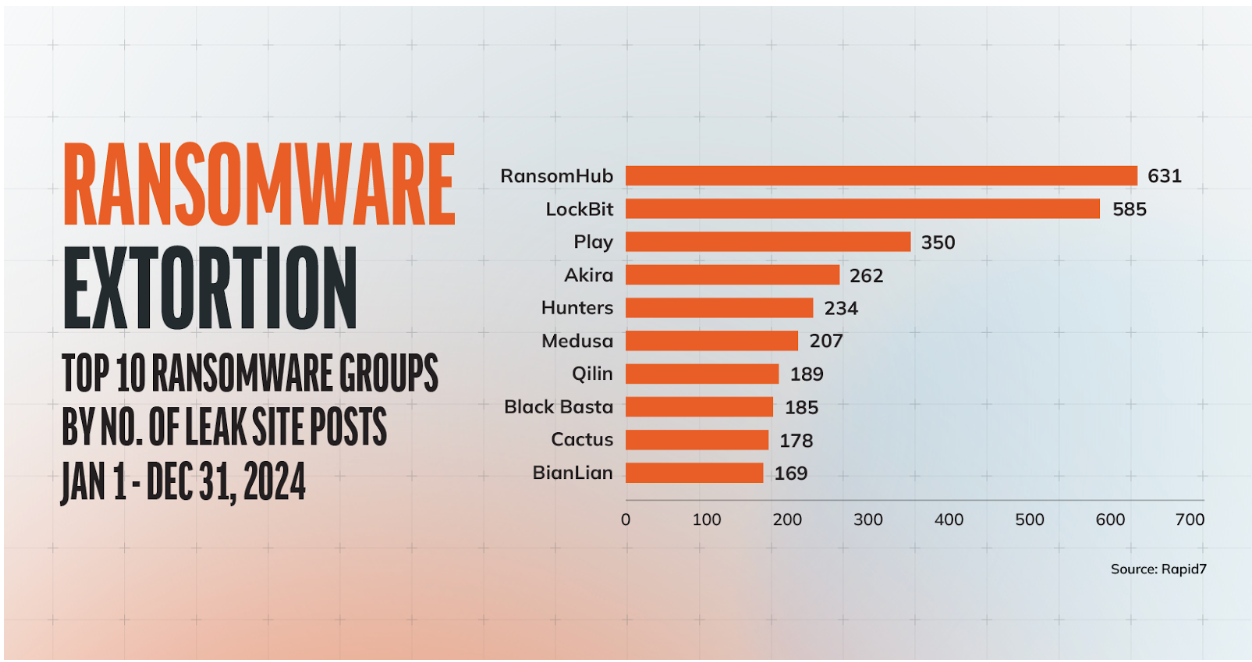
Below are the 10 most prolific ransomware groups in 2024, ranked by the number of posts on leak sites:

The 2024 Ransomware Landscape: Looking back on another painful year

While these numbers reflect public disclosures, many victims choose to negotiate privately, meaning the true scope could be significantly higher.

The Cl0p group recently disclosed exploiting a vulnerability in Cleo file transfer software, further illustrating how threat actors pivot between high-profile platform vulnerabilities with minimal downtime. While the group avoids using conventional ransomware payloads, they still rely on a leak site to extort payment from victims. Because Cl0p’s business model isn’t driven by fully encrypting victims’ data, the ransom amounts they demand — and ultimately receive — remain opaque, making it difficult to quantify their financial impact within the broader ransomware ecosystem.

Estimated Financial Impact

Based on the median payment amount of $200,000 cited above and the stat that about 32% of companies choose to pay, we can make **rough** estimates of total potential revenue generated by these groups.

Note that this calculation assumes:

  1. Each post represents one victim.
  2. 32% of those victims pay.
  3. Ransom is always $200,000.  

These assumptions likely understate the actual impact, as some victims pay more (the average is $479,237). Even so, the total in 2024 could easily exceed $380 million in ransom paid.

Group Posts 32% of Posts (Paying Victims) Hypothetical Revenue (USD)
RansomHub 631 201.92 $40,384,000
LockBit 585 187.20 $37,440,000
Play 350 112 $22,400,000
Akira 262 83.84 $16,768,000
Hunters 234 74.88 $14,976,000
Medusa 207 66.24 $13,248,000
Qilin 189 60.48 $12,096,000
Black Basta 185 59.20 $11,840,000
Cactus 178 56.96 $11,392,000
BianLian 169 54.08 $10,816,000

Table Note: These calculations are illustrative only; actual outcomes will differ.

Following are four trends we’re seeing in Rapid7 Labs, based on the global threat intelligence we gather as well as input from our internal research and open source communities.

1. Proliferation of Groups: With over 75 active groups, it’s clear that the barrier to entry for launching ransomware campaigns remains relatively low. In addition, fragmented groups are splintering and rebranding, making it more difficult to track and mitigate.

2. Persistent Dominance: Teams like RansomHub, Akira, and Fog continue to reign at the top, demonstrating sophisticated extortion strategies and steady affiliate growth.

3. Increased Transparency on the Victim Side: More organizations are disclosing breaches to comply with emerging regulations as well as to maintain customer trust. These self-reports, combined with the data ransomware actors post as a form of extortion, can give us a view of the threat. Still, not all attacks become public, obfuscating the true scale of the ransomware problem.

4. Rise of Double and Triple Extortion: Threat actors often demand multiple payments for data release, encryption keys, and in some cases, to prevent DDoS attacks or direct contact with partners and clients.

An additional observation: LockBit remained active throughout 2024, even as it became the focus of significant law enforcement attention. In a recent case, a dual Russian-Israeli national was charged for allegedly serving as a LockBit developer — an accusation that centers on crafting malicious code, overseeing affiliate activities, and orchestrating ransomware attacks worldwide. The indictments underscore intensified global cooperation, with agencies from the United States and the United Kingdom coordinating to disrupt LockBit’s infrastructure and hold key figures accountable. While LockBit continues to operate, these collective enforcement actions have highlighted the value of cross-border partnerships in mitigating ransomware threats

Building Resilience

Now that we’ve looked at some numbers and trends, let’s examine how we can use these learnings to inform decision-making and enable conversations at the executive level:

Prepare for Multiple Vectors: Ransomware attacks often begin with credential compromise, phishing campaigns, or exploitation of unpatched vulnerabilities. Build layered security defenses accordingly.

Secure Collaborations: Ensure robust security protocols with third parties, given the reliance on supply chains and outsourced IT services.

Incident Response Readiness: Create clear IR plans that include legal and public relations strategies. In addition, we highly recommend that companies hold twice-annual tabletop exercises to test the efficacy of their ransomware IR plans. Rapid containment and a well-managed response can help minimize financial and reputational damage.

Ongoing Risk Assessment: Regularly revisit threat models, especially as top-tier groups (like RansomHub or Cl0p) adopt new tactics and expand their affiliate networks.

Planning Ahead

Looking at the big picture, the financial incentives for cybercriminals are undeniable. Even if only one-third of victims pay a median of $200,000, the potential revenue surpasses $380 million — and that’s likely just the tip of the iceberg. This underscores three critical points for defenders:

1. Defense in Depth: Organizations must invest in proactive measures, from user awareness training and robust patching to strict access control and secure backups.

2. Threat Intelligence: Regularly monitor emerging ransomware groups and tactics to tailor defenses. Knowing who is targeting your industry and their methods is essential.

3. Commanding Your Attack Surface:  

In line with Rapid7’s emphasis on complete visibility and proactive security, it’s essential that organizations maintain a continuous view of their external footprint. This includes:  

– Regular Scanning: With automated tools that identify internet-facing assets and highlight newly exposed services or vulnerabilities.

– Real-time Monitoring: For detecting changes in cloud environments, development pipelines, and system deployments.

– Holistic Patch Management: To prioritize fixes based on known exploits and potential impact to reduce windows of opportunity for attackers.  

By commanding your attack surface, you can reduce the likelihood of unpatched systems and publicly exposed services becoming easy entry points for ransomware groups.

Conclusion

The 2024 ransomware landscape signals an ongoing escalation in the volume, variety, and financial impact of attacks. Groups like RansomHub, Akira, and Cl0p demonstrate how quickly affiliates can scale, while many new entrants take advantage of commoditized ransomware-as-a-service models. For organizations of all sizes, building resilience, staying informed, and preparing a strong response plan are critical steps in countering this persistent and evolving threat.

Disclaimer: The statistics and financial estimates shared in this blog are based on public data and should be considered general indicators rather than exact figures. Real-world incidents often involve factors that deviate from these simplified calculations.

Preventing unintended encryption of Amazon S3 objects

Post Syndicated from Steve de Vera original https://aws.amazon.com/blogs/security/preventing-unintended-encryption-of-amazon-s3-objects/

At Amazon Web Services (AWS), the security of our customers’ data is our top priority, and it always will be. Recently, the AWS Customer Incident Response Team (CIRT) and our automated security monitoring systems identified an increase in unusual encryption activity associated with Amazon Simple Storage Service (Amazon S3) buckets.

Working with customers, our security teams detected an increase of data encryption events in S3 that used an encryption method known as server-side encryption using client-provided keys (SSE-C). While this is a feature used by many customers, we detected a pattern where a large number of S3 CopyObject operations using SSE-C began to overwrite objects, which has the effect of re-encrypting customer data with a new encryption key. Our analysis uncovered that this was being done by malicious actors who had obtained valid customer credentials, and were using them to re-encrypt objects.

It’s important to note that these actions do not take advantage of a vulnerability within an AWS service—but rather require valid credentials that an unauthorized user uses in an unintended way. Although these actions occur in the customer domain of the shared responsibility model, AWS recommends steps that customers can use to prevent or reduce the impact of such activity.

Using active defense tools, we have implemented automatic mitigations that will help to prevent this type of unauthorized activity in many cases. These mitigations have already prevented a high percentage of attempts from succeeding, without customers taking steps to protect themselves. However, the threat actors used valid credentials, and it is difficult for AWS to reliably distinguish valid usage from malicious use. Therefore, we recommend that customers follow best practices to mitigate risk.

We recommend that customers implement these four security best practices to protect against the unauthorized use of SSE-C:

  1. Block the use of SSE-C unless required by an application
  2. Implement data recovery procedures
  3. Monitor AWS resources for unexpected access patterns
  4. Implement short-term credentials

I. Block the use of SSE-C encryption

If your applications don’t use SSE-C as an encryption method, you can block the use of SSE-C with a resource policy applied to an S3 bucket, or by a resource control policy (RCP) applied to an organization in AWS Organizations.

Resource policies for S3 buckets are commonly referred to as bucket policies and allow customers to specify permissions for individual buckets in S3. A bucket policy can be applied using the S3 PutBucketPolicy API operation, the AWS Command Line Interface (CLI), or through the AWS Management Console. Learn more about how bucket policies work in the S3 documentation. The following example shows a bucket policy that blocks SSE-C request for a bucket called your-bucket-name>.

{
    "Version": "2012-10-17",    
    "Statement": [
        {
            "Sid": "RestrictSSECObjectUploads",
            "Effect": "Deny",
            "Principal": "*",
            "Action": "s3:PutObject",
            "Resource": "arn:aws:s3:::<your-bucket-name>/*",
            "Condition": {
                "Null": {
                    "s3:x-amz-server-side-encryption-customer-algorithm": "false"
                }
            }
        }
    ]
 }

RCPs allow customers to specify the maximum available permissions that apply to resources across an entire organization in AWS Organizations. An RCP can be applied by using the AWS Organizations UpdatePolicy API operation, the AWS Command Line Interface (CLI), or through the AWS Management Console. Learn more about how RCPs work in the AWS Organizations documentation. The following example shows an RCP that blocks SSE-C requests for buckets in the organization.

{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "RestrictSSECObjectUploads",
      "Effect": "Deny",
      "Principal": "*",
      "Action": "s3:PutObject",
      "Resource": "*",
      "Condition": {
        "Null": {
          "s3:x-amz-server-side-encryption-customer-algorithm": "false"
        }
      }
    }
  ]
 }

II. Implement data recovery procedures

Without data protection mechanisms in place, data recovery times can be longer. As a data protection best practice, we recommend that you protect against data being overwritten and that you maintain a second copy of critical data.

Enable S3 Versioning to keep multiple versions of an object in a bucket, so that you can restore objects that are accidentally deleted or overwritten. It is important to note that versioning may increase storage costs, especially for applications that frequently overwrite objects in a bucket. In this case, consider implementing S3 Lifecycle policies to manage older versions and control storage costs.

Additionally, copy or take backups of critical data to a different bucket and perhaps to a different AWS account or AWS Region. To do this, you can use S3 replication to automatically copy objects between buckets. These buckets can reside in the same or in different AWS accounts, as well as in the same or in different AWS Regions. S3 replication also offers an SLA for customers that have more stringent RPO (Recovery Point Objective) and RTO (Recovery Time Objective) requirements. Alternatively, you can use AWS Backup for S3, which is a managed service that automates periodic backup of S3 buckets.

III. Monitor AWS resources for unexpected access patterns

Without monitoring, unauthorized actions on S3 buckets may go unnoticed. We recommend that you use tools such as AWS CloudTrail or S3 server access logs to monitor access to your data.

You can use AWS CloudTrail to log events across AWS services (including Amazon S3) and even combine logs into a single account to make them available to your security teams to access and monitor. You can also create CloudWatch alarms based on specific S3 metrics or logs to alert on unusual activity. These alerts can help you identify anomalous behavior quickly. You can also set up automation that uses Amazon EventBridge and AWS Lambda to automatically take corrective measures. See this topic in the S3 documentation for an example implementation of a setup used to scan all buckets across an organization and apply S3 Block Public Access.

IV. Implement short-term credentials

The most effective approach to mitigating the risk of compromised credentials is to never create long-term credentials in the first place. Credentials that do not exist cannot be exposed or stolen, and AWS provides a rich set of capabilities that alleviate the need to ever store credentials in source code or in configuration files.

IAM roles enable applications to securely make signed API requests from Amazon Elastic Compute Cloud (Amazon EC2) instances, Amazon Elastic Container Service (Amazon ECS), or Amazon Elastic Kubernetes Service (Amazon EKS) containers, or Lambda functions by using short-term credentials. Even systems outside the AWS Cloud can make authenticated calls without long-term AWS credentials by using the IAM Roles Anywhere feature. Additionally, AWS IAM Identity Center enables developer workstations to obtain short-term credentials backed by their longer-term user identities that are protected by Multi-factor Authentication (MFA).

All of these technologies rely on the AWS Security Token Service (AWS STS) to issue temporary security credentials that can control access to AWS resources without distributing or embedding long-term AWS security credentials within an application, whether in code or in configuration files.

Summary

Detecting unintended encryption techniques like this in your environment requires vigilance and support. In this post, we highlighted the most common indicators to look for. As your security teams work to constantly protect your environment, know that a number of teams at AWS—including the AWS Customer Incident Response Team (CIRT), Amazon Threat Intelligence, and services teams like the Amazon S3 team—are working diligently to innovate, collaborate, and share insights to help protect your valuable data.

In this post, we provided an update on this recent threat to customer data and highlighted four security best practices that customers can use to protect against the risk of bad actors using SSE-C to encrypt data by using lost or stolen AWS credentials.

As threat actor tactics evolve, our commitment to customer security remains unwavering. Together, we are building a more secure cloud environment, allowing you to innovate with confidence.

If you ever suspect unauthorized activity, please don’t hesitate to contact AWS Support immediately.

Steve de Vera
Steve de Vera

Steve is a manager in the AWS Customer Incident Response Team (CIRT) with a focus on threat research and threat intelligence. He is passionate about American-style BBQ and is a certified competition BBQ judge. He has a dog named Brisket.
Jennifer Paz
Jennifer Paz

Jennifer is a Security Engineer with over a decade of experience, currently serving on the AWS Customer Incident Response Team (CIRT). Jennifer enjoys helping customers tackle security challenges and implementing complex solutions to enhance their security posture. When not at work, Jennifer is an avid walker, jogger, pickleball enthusiast, traveler, and foodie, always on the hunt for new culinary adventures.

Ransomware Groups Demystified: CyberVolk Ransomware

Post Syndicated from Rapid7 Labs original https://blog.rapid7.com/2024/10/03/ransomware-groups-demystified-cybervolk-ransomware/

Ransomware Groups Demystified: CyberVolk Ransomware

As part of our ongoing efforts to monitor emerging cyber threats, we have analyzed the activities of CyberVolk, a politically motivated hacktivist group that transitioned into using ransomware and has been active since June 2024. Unlike traditional ransomware groups, CyberVolk initially positioned itself as a hacktivist organization, and then started to use ransomware as a tool for retaliation. The group openly declares allegiance to Russia and operates within a broader hacktivist movement, launching attacks in response to geopolitical events. This report offers an in-depth analysis of CyberVolk’s ransomware tactics, underlying motivations, and technical behaviors.

Rapid7 Labs has an ongoing commitment to help organizations understand and mitigate risk from the complex world of ransomware, and this includes highlighting these newer groups. In this post we’re going to focus on CyberVolk’s shift from a hacktivist group to one that now uses ransomware as a key tool in its operations.

Intro to the CyberVolk group

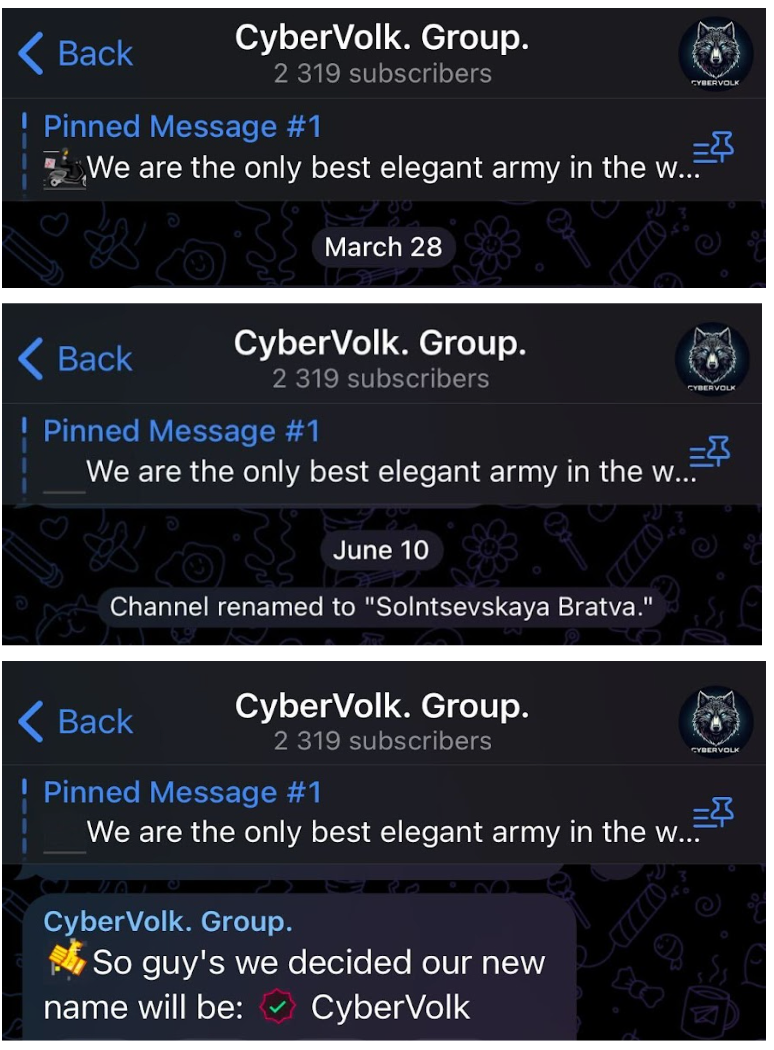
CyberVolk emerged in June 2024 as a hacktivist group associated with pro-Russian activities. Before settling on its current identity it went through several name changes. Initially known as GLORIAMIST India on March 28, 2024, the group rebranded itself as Solntsevskaya Bratva on June 10, 2024. However, this name was short-lived, and on June 23, 2024, the group adopted the name CyberVolk. Their operations escalated after the arrest of members from the hacktivist group NoName57(16), known for targeting NATO-aligned countries. In response, CyberVolk, alongside more than 70 affiliated hacktivist groups, launched coordinated Distributed Denial of Service (DDoS) and ransomware attacks against Spain, which had arrested the NoName57(16) members. These attacks are part of a broader strategy to retaliate against governments opposing Russian interests.

Ransomware Groups Demystified: CyberVolk Ransomware
Figure 1: CyberVolk’s name rebranding form March-June 2024

CyberVolk uses a combination of ransomware and DDoS attacks to undermine their targets. Spanish institutions have been a primary focus, with 27 entities reportedly affected since the campaign began.

This isn’t the first time a hacktivist group has taken a stroll down the dark side. Just last year, we covered the GhostLocker group, which made an attempt to transition from the hacktivist realm to ransomware-as-a-service (RaaS). Side bar: their debut into the ransomware world didn’t exactly go as planned. After realizing that success in the RaaS game wasn’t in their best interest, they swiftly pivoted back to their old hacktivist ways, likely with a sigh of relief. But let’s go back to the CyberVolk (with “Volk” meaning “wolf” in Russian).

Technical analysis of CyberVolk ransomware

We analyzed a sample of the CyberVolk ransomware.

| SHA256 | 102276ae1f518745695fe8f291bf6e69856b91723244881561bb1a2338d54b12 |

CyberVolk follows a standard execution flow typical to ransomware strains. One of the first actions it takes is saving an image file tmp.bmp to C:\Users\USER\AppData\Local\Temp\tmp.bmp and changing the victim’s desktop wallpaper — interestingly, this occurs before any files on the system are encrypted.

The ransomware then creates multiple threads to handle various tasks, including:

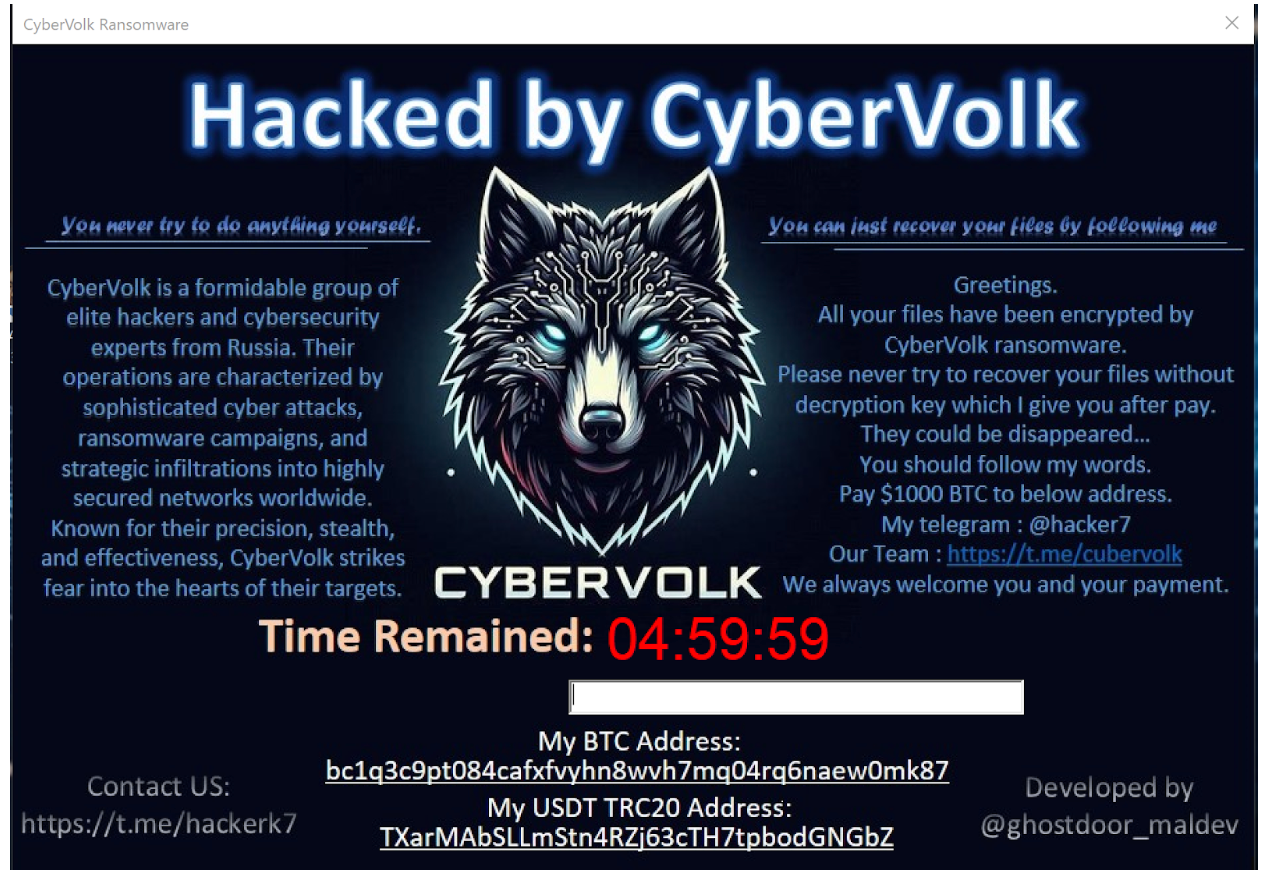
  • User interaction: A thread manages the interaction with the victim, displaying dialog boxes for the ransom message, decryption key entry, and cryptocurrency payment options for BTC (Bitcoin) and USDT ERC20. The addresses used are:
  • BTC: bc1q3c9pt084cafxfvyhn8wvh7mq04rq6naew0mk87
  • USDT: TXarMAbSLLmStn4RZj63cTH7tpbodGNGbZ At the time of writing, the BTC wallet had a balance of 0, and the USDT wallet held 34.79 USDT.
  • Task manager monitoring: Another thread checks repeatedly if Task Manager is running by searching for a window with the class name “TaskManagerWindow.” If found, it attempts to kill the process by sending a WM_CLOSE message. This action requires the ransomware to run with escalated privileges.
  • File scanning and encryption: CyberVolk performs a systematic scan of all available drive letters (from a to z) to identify valid drives for encryption. Once the encryption routine is triggered:
  • Files on the infected system are encrypted and given the .cvenc extension.
  • The ransomware methodically scans directories and subdirectories, encrypting files as it proceeds.
  • Decryption key management: After encrypting the files, CyberVolk presents the victim with an interface to input a decryption key following ransom payment. Here’s how the decryption process works:
  • Key validation: The ransomware checks if the entered decryption key is exactly 36 characters long. However, despite the full key being 36 characters, only the first 16 characters are passed to a substitution function that transforms part of the key using a predefined substitution table.
  • Substitution function: The function processes multiple encrypted string arrays and performs character substitution based on a preset character set. It compares each character from the first 16 characters of the entered key with encrypted string arrays and replaces them using the substitution table.
  • Writing the key: The transformed output is written to a file named dec_key.dat, which is then used to complete the decryption process. If the decryption key passes all checks, the ransomware decrypts the files.
  • Cleanup: After successful decryption, it removes files like dec_key.dat and time.dat from C:\Users\USER\AppData\Roaming\ to cover its tracks.
Ransomware Groups Demystified: CyberVolk Ransomware
Figure 2: CyberVolk dialog window

Experiment: Decryption key testing with CyberVolk ransomware

As part of a small experiment, we attempted to execute the CyberVolk ransomware with a pre-created dec_key.dat file placed in C:\Users\USER\AppData\Roaming\. This file contained hardcoded strings we found in the code, such as fc99bb1c28a5ae006e567faf4cfc0d707c1528e and ce12f0967bd216d248cafda3d46ad1368d9f3dee.

Upon running the malware, the presence of the file successfully triggered the decryption routine. However, despite the original file names being restored, the files themselves were empty.

In another experiment, we manually entered 36 random characters into the decryption key dialog box. Again, this triggered the decryption process, and although the file names were restored, the files remained empty.

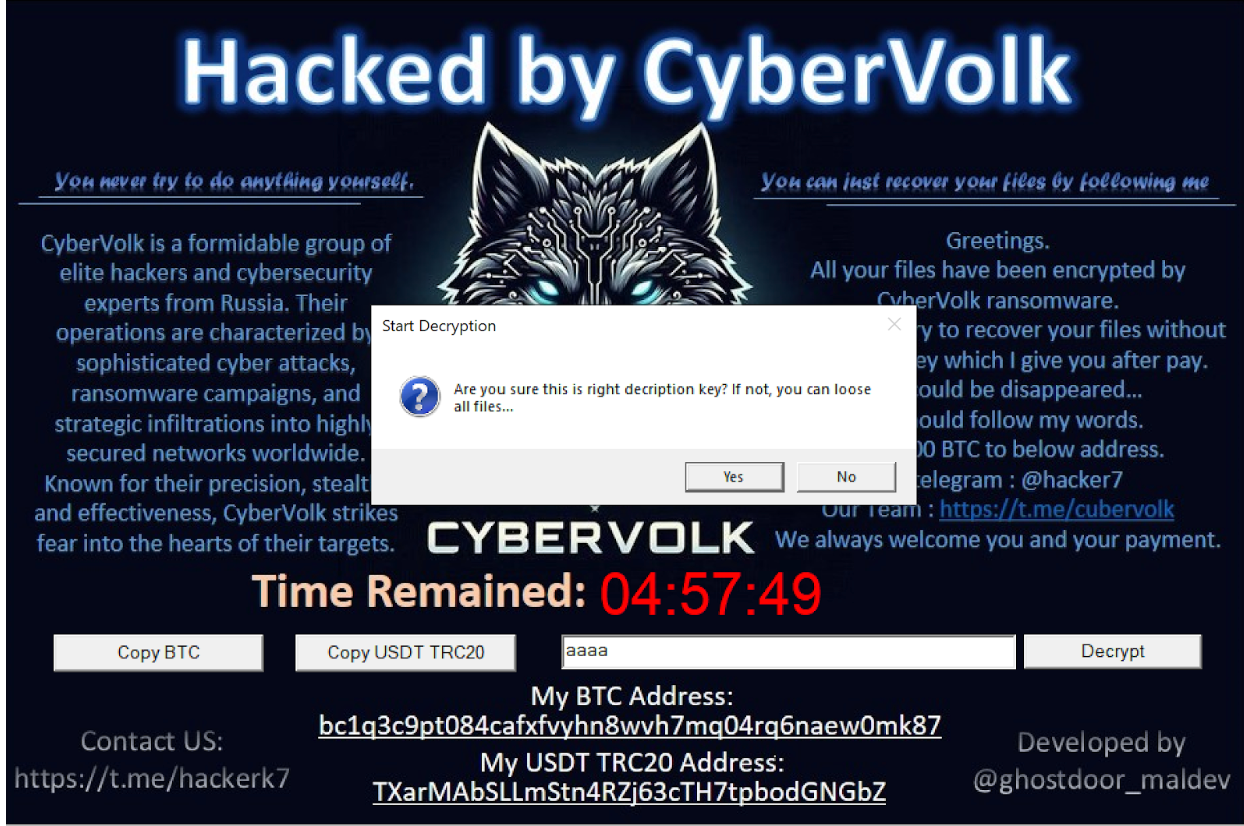
Additionally, the ransomware claims that it will delete files if an incorrect decryption key is entered. We tested this by entering an invalid key (aaaa). The malware displayed a warning, but when we proceeded, all files remained encrypted, and none were deleted.

Ransomware Groups Demystified: CyberVolk Ransomware
Figure 3: Correct key warning

CyberVolk’s decryption routine seems to have a weakness in its validation process, allowing it to proceed with decryption even with incorrect or random keys. However, without the correct key, the files are rendered unusable, suggesting that the key validation might only partially function or that the ransomware is designed to deceive victims into thinking decryption is occurring, when in reality, the files remain damaged. This could be a design flaw or a deliberate tactic to further frustrate victims.

The fact that files are not deleted as promised when an incorrect key is entered also indicates a discrepancy between the ransomware’s claims and its actual behavior. This could either be a design flaw or a deliberate tactic to further confuse and frustrate victims. Ultimately, even if the ransomware initiates decryption, without the correct key, files remain damaged and unusable.

Ransom note

After encryption, a file named CyberVolk_ReadMe.txt is placed in every affected folder. The ransom note contains the following message:

All your files have been encrypted by CyberVolk ransomware.
Do not attempt to recover your files without the decryption key, which I will provide after you make the payment.
Failure to do so may result in your files being permanently lost.
Follow my instructions carefully.

Payment Details:
Transfer $1000 in Bitcoin to the following address.
You can contact me via Telegram: @hacker7
Our team is available at https:[//]t.me/cubervolk. We look forward to receiving your payment.

The ransom note directs victims to a non-existing channel https:[//]t.me/cubervolk. Looks like the ransomware creators were in such a rush to demand the ransom that they forgot to double-check their own link.

Code reuse from Babuk ransomware

Our comparison of CyberVolk and Babuk ransomware using BinDiff revealed some similarities, particularly in cryptographic routines and system-level interactions. For example, the function CryptAcquireContextW and other cryptographic setups show significant overlap between the two, indicating that CyberVolk’s developers likely reused Babuk’s encryption framework.

However, CyberVolk has added unique functionality, such as:

  • Anti-analysis techniques: Efforts to evade detection through Task Manager termination.
  • AES encryption: Unlike Babuk, CyberVolk incorporates the AES encryption algorithm, enhancing its cryptographic capabilities and further differentiating the two strains.

Conclusion

CyberVolk ransomware shows off the usual ransomware tricks complete with a few bugs for good measure. By reusing some of Babuk’s code — particularly in its cryptographic routines — it’s clear that ransomware authors are getting creative with their remix skills, building on old frameworks to make their threats just a little more polished.CyberVolk also introduces some original features, such as attempting to terminate system processes like Task Manager. It succeeds in this task when run with elevated privileges.

Our decryption tests revealed that ransomware has some flaws. CyberVolk’s key validation is weak enough that even random keys trigger the decryption routine, though files remain unusable without the correct key. Despite its warnings about deleting files if an incorrect key is entered, we found that files remained encrypted but were not deleted, highlighting a gap between what the ransomware claims and what it actually does.

Still, CyberVolk has caused significant disruption, particularly in Spain. With its mix of DDoS and ransomware attacks, it’s becoming a more serious threat. As the group refines its tactics, cybersecurity professionals should keep a close eye on its continued evolution.

Cybersecurity professionals should keep this ransomware on their radar. Despite its bugs, CyberVolk is evolving and has already proven effective, causing significant damage to entities in Spain. It adds enough new tricks to the traditional ransomware formula to evade detection and create serious headaches for its victims.

Read up on additional ransomware groups and get other insights from Rapid7 Labs here.

Weird Zimbra Vulnerability

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/10/weird-zimbra-vulnerability.html

Hackers can execute commands on a remote computer by sending malformed emails to a Zimbra mail server. It’s critical, but difficult to exploit reliably.

In an email sent Wednesday afternoon, Proofpoint researcher Greg Lesnewich seemed to largely concur that the attacks weren’t likely to lead to mass infections that could install ransomware or espionage malware. The researcher provided the following details:

  • While the exploitation attempts we have observed were indiscriminate in targeting, we haven’t seen a large volume of exploitation attempts
  • Based on what we have researched and observed, exploitation of this vulnerability is very easy, but we do not have any information about how reliable the exploitation is
  • Exploitation has remained about the same since we first spotted it on Sept. 28th
  • There is a PoC available, and the exploit attempts appear opportunistic
  • Exploitation is geographically diverse and appears indiscriminate
  • The fact that the attacker is using the same server to send the exploit emails and host second-stage payloads indicates the actor does not have a distributed set of infrastructure to send exploit emails and handle infections after successful exploitation. We would expect the email server and payload servers to be different entities in a more mature operation.
  • Defenders protecting Zimbra appliances should look out for odd CC or To addresses that look malformed or contain suspicious strings, as well as logs from the Zimbra server indicating outbound connections to remote IP addresses.

Is Your Data Really Safe? How to Test Your Backups

Post Syndicated from David Johnson original https://www.backblaze.com/blog/is-your-data-really-safe-how-to-test-your-backups/

A decorative image showing icons related to backing up and restoring data.

Ransomware is now a billion dollar industry, and one of the best things any business can do to protect its bottom line is to back up. But, it’s important to remember that backups are only the first step in the process—when you are affected by a ransomware attack, natural disaster, or even human error, you’ll then need to restore. 

As your business scales and becomes more complex, so does your backup and restore process. You’ll have more types of data to restore, on more networks and devices, with more people involved at every step of the way. 

The best way to make sure your backups are effective? Test them regularly. Let’s talk about why and how. 

Good reasons to test your backups

By regularly testing your backups, you can improve your chances of a successful recovery and minimize the impact of data loss. Here are several reasons why regular backup testing is crucial:

  1. Data integrity verification: Testing ensures that your backups are accurate and complete. A failed test might reveal corrupted files or missing data that could lead to significant losses.
  2. Recovery process validation: By simulating the recovery process, you can identify potential bottlenecks or issues in your restoration procedures. This ensures that you can quickly and effectively recover your data in case of a disaster.
  3. Disaster readiness assessment: Regular testing helps you assess your overall disaster recovery plan. It reveals any weaknesses or gaps that need to be addressed to ensure business continuity and to meet recovery time objectives.
  4. Compliance adherence: Many industries have strict data retention and backup requirements. Testing helps you demonstrate compliance with these regulations. 
  5. Cyber insurance standards: Cyber insurance adoption is increasingly important for businesses, and many cyber insurance providers focus both on helping their clients prepare for ransomware attacks and recovery after the fact. As a result, many require regular backup verification testing and reporting. 
  6. Peace of mind: Knowing that your backups are reliable and tested can provide peace of mind and reduce stress during a crisis.
  7. Early detection of issues: Testing can uncover problems with your backup software, hardware, or processes early on, allowing you to address them before they lead to more significant consequences.

In short, regular backup testing not only confirms that your data is properly backed up, but also ensures that you’re meeting recovery point objectives (RPO), have key features like immutability configured properly, and supports overall business objectives.

Ransomware and backups

In addition to the above reasons, it’s important to note the growing trend for ransomware bad actors to specifically target backups. Veeam’s 2024 Ransomware Trends Report shows that 96% of attacks focus on backup repositories with the bad actors successfully affecting the backups in 76% of cases. Elsewhere, Sophos reports in instances where backups were compromised, ransomware demands doubled, and recovery costs were eight times higher. 

How to test your backups

Testing device backups is crucial to ensure data integrity and recoverability in case of loss or damage. Here are some effective methods:

1. Manual restoration tests

  • Regularly restore files: Select random files from your backup and restore them to a different location. Verify that the restored files are identical to the original files.
  • Test system restore: If your backup includes system images, periodically restore them to a separate partition or virtual machine to ensure they function correctly.

2. Automated testing tools

  • Backup software features: Many backup solutions offer built-in testing features. These tools can automatically verify the integrity of your backups and alert you to any issues. Restore services like Cloud Instant Backup Recovery can also provide valuable insight and support before, during, and after ransomware events. 
  • Third-party verification tools: Consider using specialized tools designed for backup verification. These tools can provide more in-depth analysis and reporting.

3. Simulated disaster scenarios 

  • Create a test environment: Set up a simulated disaster environment, such as a corrupted hard drive or a system failure.
  • Attempt recovery: Try to restore your data from the backup to the simulated environment. This will help you assess the effectiveness of your backup and recovery procedures.

4. Cloud-based backup testing for different recovery scenarios

  • Restore workstations: If you use cloud backup for your workstations, test restoring your files to a new device. This will show the functionality of the cloud backup service and ensure that your data can be accessed and restored successfully.
  • Restore server or network data: In addition to endpoints, you’ll also want to restore your servers or networks to different business locations. This lets you pressure test the cost of restores to account for things like hidden fees, and to ensure functions like immutability are properly configured.   

5. Regular backup verification

  • Check file integrity: Regularly verify the integrity of your backup files using checksums or hash functions. This will help detect any corruption or damage that may have occurred.
  • Review backup logs: Monitor your backup logs for any errors or warnings that might indicate issues with the backup process.

By following these methods, you can ensure that your device backups are reliable and that you can recover your data effectively in case of a disaster.

The human element

Don’t forget that this includes things like establishing where and how you’ll communicate if, for instance, company email is offline. It’s also important to designate incident managers to streamline decision making and ensure that essential personnel have the access and permissions they need. 

How cloud storage can help

Store your backup data in readily accessible, hot storage. This minimizes retrieval times during a disaster, enabling faster recovery of critical applications and data. 

By implementing a robust backup strategy that incorporates the 3-2-1 backup rule (or, the more robust, and increasingly enterprise standard 3-2-1-1-0 method), immutability, version control, and cloud storage, you can ensure the protection of your critical data against various threats. And, by testing frequently, you can rely on the fact that those backups—and your team—are ready to get your business back online as soon as possible.

The post Is Your Data Really Safe? How to Test Your Backups appeared first on Backblaze Blog | Cloud Storage & Cloud Backup

Our 4 Essential Strategy Takeaways from the Gartner® 2024 Report – How to Prepare for Ransomware Attacks

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/09/09/our-4-essential-strategy-takeaways-from-the-gartner-r-2024-report-how-to-prepare-for-ransomware-attacks/

Our 4 Essential Strategy Takeaways  from the Gartner® 2024 Report – How to Prepare  for Ransomware Attacks

As ransomware threats continue to evolve, security and risk management leaders must stay ahead by adopting comprehensive strategies to protect their organizations. The 2024 Gartner report, “How to Prepare for Ransomware Attacks”, provides critical insights into the latest tactics used by bad actors and offers practical solutions on how to fortify defenses.

Below, we highlight our four key strategy takeaways  from the report to help your organization prepare for and respond to ransomware attacks.

Adapt to the rise of extortionware

Traditional ransomware tactics are shifting towards extortionware—where attackers steal data and demand payment for its destruction rather than encrypting it. This growing threat emphasizes the need for robust data protection strategies.

According to Gartner: “Extortionware (encryption-free, data theft attack) is a growing tactic being used by bad actors.”

This evolution in tactics, which includes the emergence of 21 new ransomware groups in the first half of 2024, as noted in Rapid7’s Ransomware Radar Report, underscores the need for organizations to continuously update their defenses to counter new threats.

Actionable Strategy: Regularly update your threat models and security measures to account for new and emerging ransomware groups. Invest in advanced threat intelligence to stay informed about the latest tactics used by these criminal enterprises.

Strengthen your defenses with advanced detection technologies

This is increasingly important as ransomware attacks are becoming more frequent and sophisticated. Rapid7’s research highlights a 23% increase in ransomware posts on leak sites during the first half of 2024, further emphasizing the growing threat landscape.

We believe Gartner reinforces the importance of detection, stating: “… identity threat detection and response (NDR) tools  collect indicators of compromise (IOCs) and events that alert you to anomalous behaviors that could indicate that an attack ‘may’ be underway.”

In addition to these detection tools, Gartner advises that a defense strategy should include Endpoint Protection Platforms (EPPs), EDR, and mobile threat defense (MTD) solutions.

For organizations lacking the necessary in-house expertise or resources, Gartner recommends supplementing EDR with managed services: “If internal teams don’t have the necessary skill set or bandwidth, supplement EDR with managed services (see Market Guide for Managed Detection and Response Services).”

Actionable strategy: Implement and regularly update behavioral-anomaly-based detection technologies. Ensure that your security operations center (SOC) is equipped to respond swiftly to any detected threats.

Rapid7’s Managed Threat Complete, which integrates core MDR functionality with transparency into operations and technology, ensures comprehensive visibility across endpoints, networks, users, and cloud infrastructure. We believe this aligns with the Gartner recommendation to supplement EDR with managed services to enhance your organization’s security posture (see the Gartner Market Guide for Managed Detection and Response Services).

Pay attention to vulnerable targets

While large organizations are often targeted, mid-sized companies are increasingly vulnerable to ransomware attacks. Rapid7’s findings support this, showing that companies with $5 million in annual revenue are being attacked up to five times more often than larger enterprises. These organizations are particularly attractive to attackers due to their valuable data and often less mature security defenses.

Actionable strategy: Mid-sized organizations should prioritize investing in mature cybersecurity defenses, particularly in endpoint protection, identity management, and regular security training for employees.

You can view the Rapid7 Ransomware Radar Report here.

Pay attention to vulnerable targets

While large organizations are often targeted, mid-sized companies are increasingly vulnerable to ransomware attacks. Rapid7’s findings support this, showing that companies with $5 million in annual revenue are being attacked up to five times more often than larger enterprises. These organizations are particularly attractive to attackers due to their valuable data and often less mature security defenses.

Actionable strategy: Mid-sized organizations should prioritize investing in mature cybersecurity defenses, particularly in endpoint protection, identity management, and regular security training for employees.

You can view the Rapid7 Ransomware Radar Report here.

Prepare with a comprehensive ransomware playbook

One of the key insights from the Gartner research is the critical importance of having a well-prepared incident  response plan. Given the increasingly sophisticated nature of ransomware groups—many of which now operate like full-fledged businesses with their own marketplaces and support networks—a detailed and rehearsed ransomware playbook is essential for any organization.

Gartner  states: “Develop an incident response plan with containment strategies that is augmented with a ransomware playbook.”

Actionable strategy: Develop and regularly update a ransomware playbook that includes clear roles, decision-making protocols, and communication plans. Conduct regular tabletop exercises to ensure your team is prepared to act swiftly and effectively.

Conclusion: fortify your defenses against ransomware

Ransomware is an ever-present threat that requires a proactive, multi-layered approach to defense. We feel the 2024 Gartner Report “How to Prepare for Ransomware Attacks” provides essential strategies for preparing, detecting, and responding to these attacks. By implementing these recommendations, we believe your organization can better protect itself against the evolving tactics of cybercriminals.

Download the full Gartner report to explore detailed insights and recommendations for strengthening your ransomware defenses.

Gartner, Inc. How to Prepare for Ransomware Attacks. Paul Furtado. 16 April 2024.

GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the

U.S. and internationally and is used herein with permission. All rights reserved.

Security Researcher Sued for Disproving Government Statements

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/09/security-researcher-sued-for-disproving-government-statements.html

This story seems straightforward. A city is the victim of a ransomware attack. They repeatedly lie to the media about the severity of the breach. A security researcher repeatedly proves their statements to be lies. The city gets mad and sues the researcher.

Let’s hope the judge throws the case out, but—still—it will serve as a warning to others.

Selling Ransomware Breaches: 4 Trends Spotted on the RAMP Forum

Post Syndicated from Christiaan Beek original https://blog.rapid7.com/2024/08/20/selling-ransomware-breaches-4-trends-spotted-on-the-ramp-forum/

Selling Ransomware Breaches: 4 Trends Spotted on the RAMP Forum

The sale and purchase of unauthorized access to compromised enterprise networks has become a linchpin for cybercriminal operations, particularly in facilitating ransomware attacks. Underground forums are sharing guidelines on breaching networks and selling the access they obtain, leaving the exploitation to other malicious actors.

On underground criminal forums, these transactions allow actors with complementary skills to collaborate, amplifying the impact and reach of cyberattacks. The market for such access has grown notably, especially as ransomware operators increasingly employ double-extortion tactics. A foothold in a victim’s network, with credentials that enable stealthy operations, has never been a more lucrative — and popular — business model.

Organizations across all sectors and regions are vulnerable and a target. The collective shift to remote work during the COVID-19 pandemic has expanded the attack surface, as more remote access tools remain in use to this day. In our 2024 Attack Intelligence Report, we noted that 36% of all widespread threat events Rapid7 tracked in 2023 involved the exploitation of network edge device vulnerabilities. This trend has continued into 2024.

In this blog, we delve into a major forum frequented by ransomware actors and affiliates, called RAMP. As part of our research for the Rapid7 Ransomware Radar Report, we analyzed RAMP postings offering corporate access from January 1, 2024 to June 30, 2024, uncovering 4 key trends within this underground marketplace.

The forum: RAMP

Re-launched/branded in July 2021, the RAMP (Ransomware and Advanced Malware Protection) forum is an underground cybercriminal hub originally known as Payload.bin, tracing its roots back to 2012 when it first operated on the Tor network. With a primary focus on ransomware, RAMP is a multilingual platform catering to Russian, Chinese, and English speakers and boasts over 14,000 registered members. Access to RAMP is highly restricted; potential users must have been active members on the XSS and Exploit forums for at least two months, have posted at least ten times, and maintain a good reputation, or alternatively, pay a $500 registration fee for anonymity.

Selling Ransomware Breaches: 4 Trends Spotted on the RAMP Forum

RAMP serves as both a forum and a marketplace, offering ransomware kits, malware, and stolen data, while also providing comprehensive guides and tutorials for cyberattacks. It facilitates ransomware-as-a-service (RaaS) operations, enabling affiliates to deploy ransomware for a share of the profits. Despite its high registration fee, a stark contrast to the $120 annual fee for premium XSS users, RAMP’s closed community is a critical resource for many threat actors. The forum’s design mimics Silk Road-like darknet markets, including escrow features, and it operates primarily off-the-record to avoid law enforcement detection. Its administrator claims an annual revenue of around $250,000, benefiting from its predominantly Russian user base and a strict policy against selling certain illegal goods and services.

Selling Access

To investigate the trends and context around the selling of access into corporate networks, we analyzed all the postings on the RAMP forum from January through June 2024. Some of these posts were cross-posted on other underground forums as well. In most of the cases, the initial access was mentioned and/or the price asked. Where this data was not available, we classified that as ‘unknown’ in our dataset for analysis.

Selling Ransomware Breaches: 4 Trends Spotted on the RAMP Forum

So what are some of the trends we discovered?

Trend #1: Country Distribution

The United States leads the pack with the highest number of entries referencing the country of the company attackers have credentials or access to, followed by France and Brazil. Companies based in Western countries command a higher price due to their perceived wealth and easier access to resources for payment, so what we’re seeing thus far in 2024 (per the chart below) is what would be expected. The only exception to this is Brazil, likely due to Brazilian affiliates that target larger Brazilian businesses.

Selling Ransomware Breaches: 4 Trends Spotted on the RAMP Forum

Trend #2: Revenue Distribution

One of the variables that determine the asking price for network access is the revenue made by the target. Very often, sites like ZoomInfo are used to look up the annual revenue, which is then mentioned in the posting, as in our example below.

Selling Ransomware Breaches: 4 Trends Spotted on the RAMP Forum

As the chart below shows, we observed a broad range of revenue values within the RAMP dataset, where some entries specified exact amounts and others used ranges. A significant number of entries included revenues in the millions, particularly around $5 million USD.

In fact, companies with revenues in the $5 million range appeared twice as often as those in the $30-50 million range and 5 times more frequently than those with a $100 million revenue. This could indicate that such companies are large enough to hold valuable data but perhaps not as well protected as larger corporations. Regardless, this finding shows that companies with $5 million in revenue are attractive targets and represents an interesting shift from access brokers only targeting the “big fish.”

Selling Ransomware Breaches: 4 Trends Spotted on the RAMP Forum

Trend #3: Access Type Distribution

How are threat actors getting in? Our analysis shows that Remote Desktop Protocol (RDP) is the most common access type, followed by VPN. VPN presents a greater possibility of remaining undetected. That, in combination with the level of access (user or privileged user), demands a higher price.

Selling Ransomware Breaches: 4 Trends Spotted on the RAMP Forum

RDP is often used for remote work and system management, and it can be a significant vulnerability if not properly secured. The prevalence of RDP underscores the importance of securing remote access points.

As noted in our 2024 Attack Intelligence Report, missing or unenforced multi-factor authentication (MFA) gave rise to 41% of the incidents Rapid7 MDR observed in 2023. Companies should ensure robust security measures like MFA and proper network segmentation to protect RDP endpoints. Also, if we consider the combined value of VPN and such technologies, then the trend of targeting network edge devices will certainly continue.

Trend #4: Price Distribution

Many RAMP entries list unknown prices. Among the known prices, amounts like $500, $800, and $1000 are common. Company revenue, headquarter location, and the type of access are each a basis for how the threat actor formulates their asking price, which can range widely based on the perceived value of the target network. It is common for prices to spike based on the specific attributes of the target (e.g., revenue, security posture, type of data accessible).

Conclusion

Our analysis highlights key areas of concern for companies looking to protect themselves against access brokers. Businesses in the US, France, and Brazil, as well as those with revenues around $5 million, should be particularly vigilant. Securing remote access points, investing in robust solutions, and understanding the pricing dynamics of the black market for network access can help companies bolster their defenses against this pervasive threat.

By staying informed about these and other ransomware trends, businesses can better understand the risks and implement effective measures to safeguard their networks against unauthorized access.

If your organization needs assistance responding to a ransomware incident, Rapid7 Incident Response can help.

The State of Ransomware

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/08/the-state-of-ransomware.html

Palo Alto Networks published its semi-annual report on ransomware. From the Executive Summary:

Unit 42 monitors ransomware and extortion leak sites closely to keep tabs on threat activity. We reviewed compromise announcements from 53 dedicated leak sites in the first half of 2024 and found 1,762 new posts. This averages to approximately 294 posts a month and almost 68 posts a week. Of the 53 ransomware groups whose leak sites we monitored, six of the groups accounted for more than half of the compromises observed.

In February, we reported a 49% increase year-over-year in alleged victims posted on ransomware leak sites. So far, in 2024, comparing the first half of 2023 to the first half of 2024, we see an even further increase of 4.3%. The higher level of activity observed in 2023 was no fluke.

Activity from groups like Ambitious Scorpius (distributors of BlackCat) and Flighty Scorpius (distributors of LockBit) has largely fallen off due to law enforcement operations. However, other threat groups we track such as Spoiled Scorpius (distributors of RansomHub) and Slippery Scorpius (distributors of DragonForce) have joined the fray to fill the void.

Key Takeaways From The Take Command Summit: Unlocking Security Success

Post Syndicated from Emma Burdett original https://blog.rapid7.com/2024/08/09/key-takeaways-from-the-take-command-summit-unlocking-security-success/

Key Takeaways From The Take Command Summit: Unlocking Security Success

As cybersecurity threats continue to evolve, so must our defenses. The recent Rapid7 Take Command Summit provided invaluable insights into preparing for, responding to, and recovering from ransomware attacks. Here are three essential takeaways from the session, “Before, During, & After Ransomware Attacks,” that every cybersecurity professional should consider.

1. Proactive Defense is Crucial: Fortify your defenses before an attack happens.. According to the panel, comprehensive security measures such as regular patching, network segmentation, and user training are vital. Implementing endpoint detection and response solutions can significantly reduce vulnerabilities. Eddie Bobritsky said, “prevention is always coming before detection and response. Investing in proactive measures is crucial.”

2. Swift Decision-Making During an Attack: During an attack, immediate and decisive action is paramount. Establishing clear protocols and communication channels can mitigate damage effectively. The panel highlighted the importance of isolating infected systems and restricting network access to contain the threat. Robert Knapp said, “swift decision-making is key to minimizing impact and ensuring a successful investigation.”

3. Building Resilience After an Attack: Recovery is a multifaceted effort. Conducting thorough forensic analysis to identify the root causes of the attack and implementing robust data backup and recovery processes are essential steps. Lonnie Best said, “building resilience against the recurrence of ransomware attacks requires proactive security measures and regular security assessments.”

Key Statistics

  • 65% of organizations impacted by ransomware in 2023 faced more than 6 days of downtime.
  • Ransomware payments were said to have topped $1 billion in 2023.
  • Rapid7 tracked 5600 reported ransomware cases between January 2023 and February 2024.

No matter how much you invest in the before stage, it will always be cheaper than dealing with it afterwards.” – Eddy Bobritsky, Senior Director, Product Management, Rapid7

Ransomware attacks are a significant threat, but with the right strategies and proactive measures, organizations can enhance their defenses and build resilience. To dive deeper into these strategies and hear more from the experts, watch the full video from the Rapid7 Take Command Summit.

Rapid7’s Ransomware Radar Report Shows Threat Actors are Evolving …Fast.

Post Syndicated from Tom Caiazza original https://blog.rapid7.com/2024/08/06/rapid7s-ransomware-radar-report-shows-threat-actors-are-evolving-fast/

Rapid7’s Ransomware Radar Report Shows Threat Actors are Evolving …Fast.

Few issues keep cybersecurity professionals up at night more than the threat of ransomware. The ubiquity of targets, the relative organization of threat actors, and their multiple paths of entry make combating ransomware particularly formidable.

But there is one more facet to this threat that makes ransomware a vexing problem across all organizations: it’s evolving, constantly.

In a new report released today by Rapid7 Labs, researchers, threat intelligence experts, and detection & response teams have put together the latest state-of-play in the ransomware space. The Ransomware Radar Report offers some startling insights into who ransomware threat actors are and how they’ve been operating in the first half of 2024.

The fact of the matter is, ransomware as a business is booming. Over the first half of 2024, Rapid7 researchers found an increase of 23% in the number of posts ransomware groups were making to their leak sites. This correlates with the amount of extortion attempts these groups are attempting as they are rarely quiet about who they infiltrate. Surprisingly, one of the newest groups, RansomHub, made the second-most number of posts among the groups studied, with 181 over that six-month period. But, to put that into perspective, the leader, well-established LockBit, made 474 posts over the same time period.

This leads us to another intriguing finding: the number of new (or revamped) ransomware groups. We found that among a total of 68 unique groups posting extortion attempts, some 21 were either net new or rebranded from previous groups. The rebranded groups may indicate a bit of a silver lining as they are potentially due to the success of some recent law enforcement actions against ransomware threat actors.

However, threat actors are only half of the equation. The report also notes that the ransomware ecosystem may be moving away from the attacks on “big fish” we had seen in the past and toward smaller organizations as juicier targets. For instance, organizations with $5 million in annual revenue were five times more likely to be targeted than their larger counterparts. This could be for a lot of reasons, not the least of which is that these smaller organizations contain many of the same data threat actors are after, but they often have less mature security precautions in place.

Ransomware actors are also getting more sophisticated as businesses. They have their own marketplaces, sell their own products, and in some cases have 24/7 support. They also seem to be creating an ecosystem of collaboration and consolidation in the kinds of ransomware they deploy. Rapid7 researchers looked at different ransomware variants and found three distinct clusters of similarities. Essentially, many of these ransomware strains resemble one another. This could indicate collaboration among groups, reuse of source code, or the use of common builders. Other research avenues indicated that the number of ransomware families is going down — potentially showing that threat actors are focusing their efforts on more effective or specialized approaches.

The takeaways in this blog post are only the tip of the iceberg. The Ransomware Radar Report goes deep into the kinds of encryption algorithms that are trending at the moment and why, details on prevailing coding languages, and the varied tactics threat actors use to infiltrate organizations. To get the latest on ransomware and ensure your organization is well-informed and prepared for the fight against these threat actors, download the report here.

VMware ESXi CVE-2024-37085 Targeted in Ransomware Campaigns

Post Syndicated from Rapid7 original https://blog.rapid7.com/2024/07/30/vmware-esxi-cve-2024-37085-targeted-in-ransomware-campaigns/

VMware ESXi CVE-2024-37085 Targeted in Ransomware Campaigns

On Monday, July 29, Microsoft published an extensive threat intelligence blog on observed exploitation of CVE-2024-37085, an Active Directory integration authentication bypass vulnerability affecting Broadcom VMware ESXi hypervisors. The vulnerability, according to Redmond, was identified in zero-day attacks and has evidently been used by at least half a dozen ransomware operations to obtain full administrative permissions on domain-joined ESXi hypervisors (which, in turn, enables attackers to encrypt downstream file systems). CVE-2024-37085 was one of multiple issues fixed in a June 25 advisory from Broadcom; it appears to have been exploited as a zero-day vulnerability.

Per Broadcom’s advisory, successful exploitation of CVE-2024-37085 allows attackers “with sufficient Active Directory (AD) permissions to gain full access to an ESXi host that was previously configured to use AD for user management by re-creating the configured AD group (‘ESXi Admins’ by default) after it was deleted from Active Directory.”

Notably, Broadcom’s advisory differs from Microsoft’s description, which says: “VMware ESXi hypervisors joined to an Active Directory domain consider any member of a domain group named "ESX Admins" to have full administrative access by default. This group is not a built-in group in Active Directory and does not exist by default. ESXi hypervisors do not validate that such a group exists when the server is joined to a domain and still treats any members of a group with this name with full administrative access, even if the group did not originally exist.”

Also of note: While the VMware advisory indicates ESXi Admins is the default AD group, the Microsoft observations quoted in this blog all indicate use of ESX Admins rather than ESXi Admins.

ESXi hypervisors have been a popular target for ransomware groups in years past. Notably, since ESXi should not be internet-exposed, we would not expect CVE-2024-37085 to be an initial access vector — adversaries will typically need to have already obtained a foothold in target environments to be able to exploit the vulnerability to escalate privileges.

Exploitation

Microsoft researchers discovered CVE-2024-37085 after it was used as a post-compromise attack technique used by a number of ransomware operators, including Storm-0506, Storm-1175, Octo Tempest, and Manatee Tempest. The attacks Microsoft observed included use of the following commands, which first create a group named “ESX Admins” in the domain and then adds a user to that group:

net group “ESX Admins” /domain /add
net group “ESX Admins” username /domain /add

Microsoft identified three methods for exploiting CVE-2024-37085, including the in-the-wild technique described above:

  • Adding the “ESX Admins” group to the domain and adding a user to it (observed in the wild): If the “ESX Admins” group doesn’t exist, any domain user with the ability to create a group can escalate privileges to full administrative access to domain-joined ESXi hypervisors by creating such a group, and then adding themselves, or other users in their control, to the group.
  • Renaming any group in the domain to “ESX Admins” and adding a user to the group or using an existing group member: This requires an attacker to have access to a user that has the capability to rename arbitrary groups (i.e., by renaming one of them “ESX Admins”). The threat actor can then add a user, or leverage a user that already exists in the group, to escalate privileges to full administrative access.
  • ESXi hypervisor privileges refresh: Even if the network administrator assigns any other group in the domain to be the management group for the ESXi hypervisor, the full administrative privileges to members of the “ESX Admins” group are not immediately removed and threat actors still could abuse it.

Mitigation guidance

The following products and versions are vulnerable to CVE-2024-37085:

The Broadcom advisory on CVE-2024-37085 links to a workaround that modifies several advanced ESXi settings to be more secure; the workaround page notes that for all versions of ESXi (prior to ESXi 8.0 U3), “several ESXi advanced settings have default values that are not secure by default. The AD group "ESX Admins" is automatically given the VIM Admin role when an ESXi host is joined to an Active Directory domain.”

Broadcom VMware ESXi and Cloud Foundation customers should update to a supported fixed version as soon as possible. Administrators who are unable to update should implement workaround recommendations in the interim. ESXi servers should never be exposed to the public internet. Microsoft has additional recommendations on mitigating risk of exploitation in their blog.

Rapid7 customers

InsightVM and Nexpose customers who use ESXi hypervisors within their environments can assess their exposure to CVE-2024-37085 for the 8.x version stream with a vulnerability check available since June 2024. Support for scanning 7.0 is expected to be available in the July 30 content release.

InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on behavior related to this vulnerability:

  • Attacker Technique – Creation of "ESX Admins" Domain Group using Net.exe

Is Ransomware Protection Working?

Post Syndicated from Bozho original https://techblog.bozho.net/is-ransomware-protection-working/

Recently an organization I’m familiar with suffered a ransomware attack. A LockBit ransomware infected a workstation and spread to a few servers. The attack was contained thanks to a quick incident response, but there was one important thing: the organization had a top-notch EDR installed. It’s in the Gartner’s leader quadrant for endpoint protection platforms. And it didn’t stop it. I won’t mention names, because the point here is not to attack a particular brand, but the fact that the attackers created a different build of the LockBit codebase meant that the signature-based detection didn’t work and so the files on the endpoints were encrypted. Not only that – attackers downloaded port scanners and executed password spraying on the network, in order to pivot to the servers, without much trouble caused by the EDR.

Ransomware is the most widespread type of attack, we have a security industry that’s trying to cope with those attacks for a long time, and in 2024 it’s sufficient to just rebuild the ransomware from source in order to not get caught. That’s a problem. To add insult to injury, the malware executable was called lockbit.exe_.

I think we need to think of better ways to tackle ransomware. I’m not an antivirus/EDR in-depth expert, but I have been thinking the following: why doesn’t the operating system have a built-in anti-ransomware functionality? The malware can stop endpoint agents, but it can’t stop the OS (well, it can stop OS services or modify OS dlls, I agree). I was thinking of native NTFS listeners to detect ransomware behavior – very fast enumeration and modification of files. Then I read this article titled “Microsoft Can Fix Ransomware Tomorrow” which echoed my thoughts. It’s not that simple as the title implies, and the article goes to argue that it’s hard, but something has to be done.

This may seriously impact the EDR market – if the top threat – ransomware – is automatically contained by built-in functionality, why purchase an EDR? Obviously, there are many other reasons to do so, but every budget cut will start from the EDR. Ransomware has been a successful driver for more investment in security. To prevent putting too much functionality in the OS, EDRs can tap into the detection capability of the OS to take further actions.

But ransomware works in a very simple way. Detecting mass-encryption of files is easy. Rate-limiting it is reasonable. You may be aware, but CPUs have AES-specific instructions that improve the performance of AES encryption – the fact that these instructions are used may be a further indicator of an ongoing ransomware attack.

I think we have to tap into the lower levels of our software stack – file system, OS, CPU – in order to tackle ransomware. It’s clear that omnipotent endpoint agents don’t exist, no matter how much “AI magic” you sprinkle ontop of them in the data sheet (I remember once asking another EDR vendor on a conference how exactly their AI is working. My impression from the answer was: it’s rules).

As I said, I’m no AV/EDR expert, and I expect comments like “But we are already doing that”. I’m sure APIs like this one are utilized by AV/EDRs, but they may be too slow or too heavy to be used. And it may mean that this APIs can be optimized for the ransomware-detection usecase. I don’t have a ready answer (otherwise I’d be an EDR vendor), but I’d welcome a serious discussion on that. We can’t be in a situation where purchasing an expensive security tool doesn’t reliably solve the most prominent threat – “off-the-shelf” ransomware.

The post Is Ransomware Protection Working? appeared first on Bozho's tech blog.

FBI Seizes BreachForums Website

Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2024/05/fbi-seizes-breachforums-website.html

The FBI has seized the BreachForums website, used by ransomware criminals to leak stolen corporate data.

If law enforcement has gained access to the hacking forum’s backend data, as they claim, they would have email addresses, IP addresses, and private messages that could expose members and be used in law enforcement investigations.

[…]

The FBI is requesting victims and individuals contact them with information about the hacking forum and its members to aid in their investigation.

The seizure messages include ways to contact the FBI about the seizure, including an email, a Telegram account, a TOX account, and a dedicated page hosted on the FBI’s Internet Crime Complaint Center (IC3).

“The Federal Bureau of Investigation (FBI) is investigating the criminal hacking forums known as BreachForums and Raidforums,” reads a dedicated subdomain on the FBI’s IC3 portal.

“From June 2023 until May 2024, BreachForums (hosted at breachforums.st/.cx/.is/.vc and run by ShinyHunters) was operating as a clear-net marketplace for cybercriminals to buy, sell, and trade contraband, including stolen access devices, means of identification, hacking tools, breached databases, and other illegal services.”

“Previously, a separate version of BreachForums (hosted at breached.vc/.to/.co and run by pompompurin) operated a similar hacking forum from March 2022 until March 2023. Raidforums (hosted at raidforums.com and run by Omnipotent) was the predecessor hacking forum to both version of BreachForums and ran from early 2015 until February 2022.”