Businesses around the world use WhatsApp as a primary channel to connect with customers. It’s familiar, trusted, and effective for everything from booking confirmations to customer support. But most of these conversations are still text-only. For many customers, text is fast and efficient. Yet there are times when typing is inconvenient, slow, or less effective at conveying nuance. In those moments, voice messages can transform the interaction — making it faster, more inclusive, and more human.
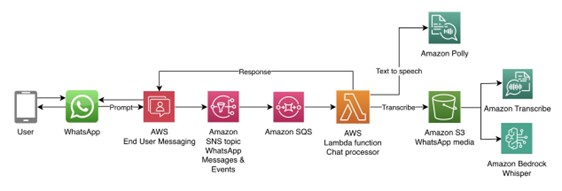
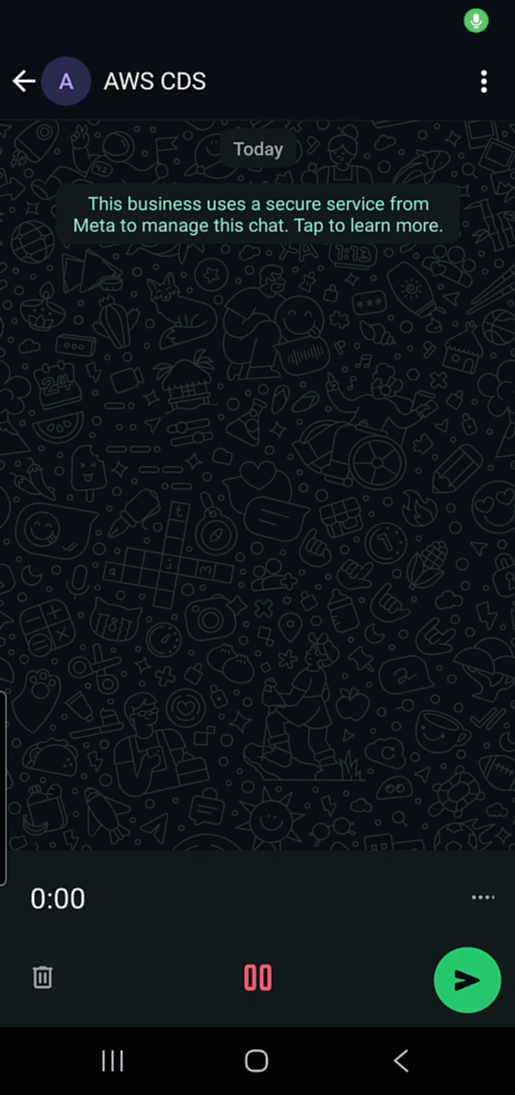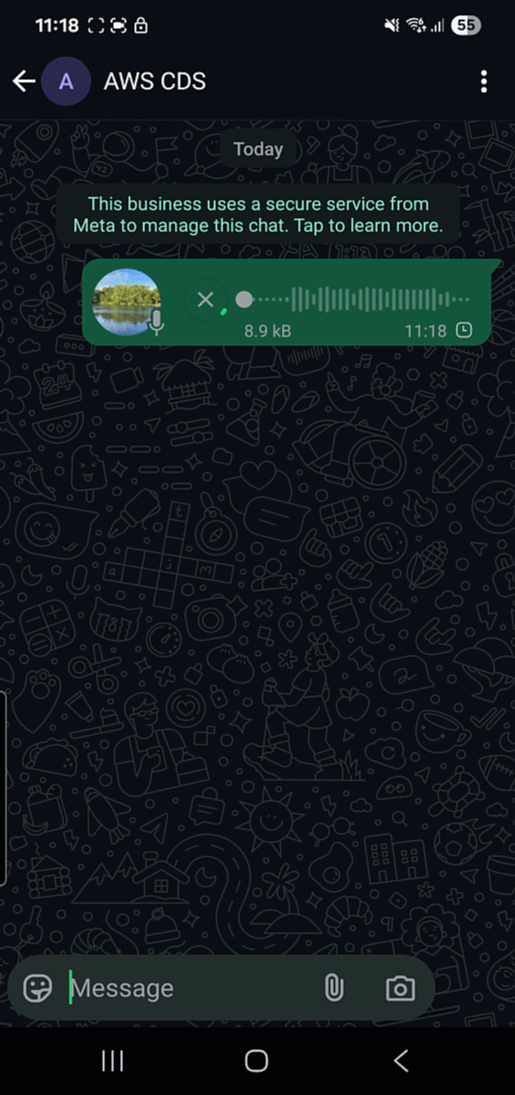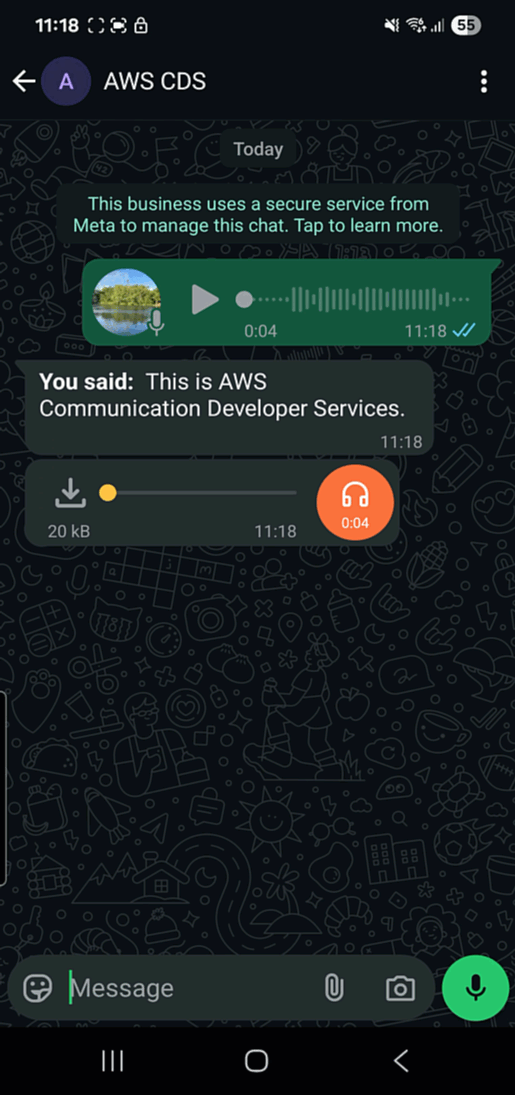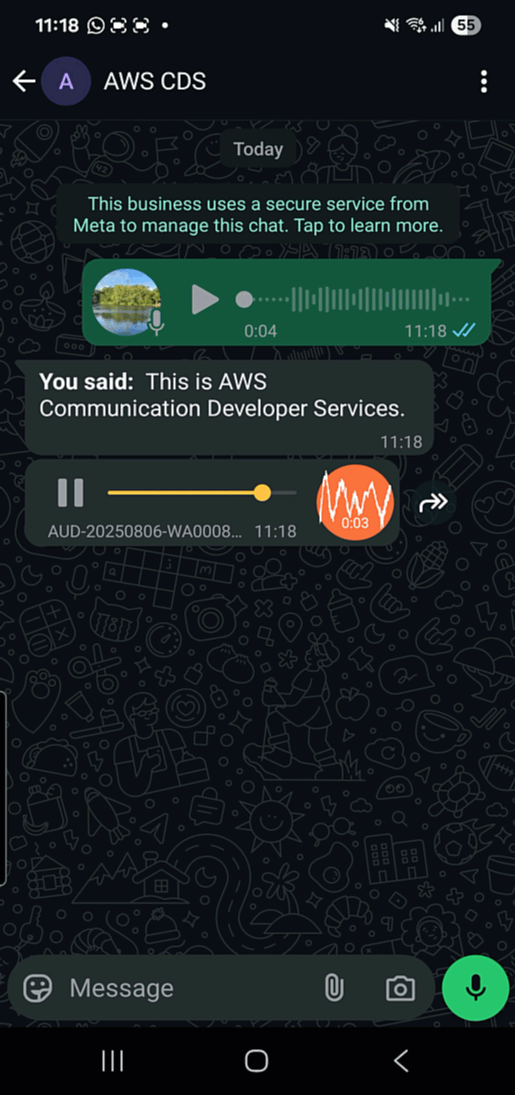
With AWS End User Messaging, businesses can now enable both voice note input and voice note responses on WhatsApp. Customers send a voice note, and a bot can respond with a natural-sounding voice note reply. Note: This solution processes asynchronous voice notes (recorded audio messages), not real-time voice calls. In this blog post, we explore why voice notes matter, where they make a difference, and how AWS helps you enable them through a sample voice note messaging solution.
Text remains essential, but research shows that voice notes adds unique advantages:
Richer communication: Voice carries tone, urgency, and emotion — reducing misunderstandings and helping businesses respond more appropriately (Preply survey).
Natural and fast: Speaking is up to three times faster than typing on mobile devices, especially when users are on the go (Sherry Ruan, Jacob O. Wobbrock, Kenny Liou, Andrew Ng, and James A. Landay. 2018. Comparing Speech and Keyboard Text Entry for Short Messages in Two Languages on Touchscreen Phones. Proc. ACM Interact. Mob. Wearable Ubiquitous Technol. 1, 4, Article 159 (December 2017), 23 pages. https://doi.org/10.1145/3161187).
Accessibility and inclusivity: Voice lowers barriers for people with limited literacy or visual impairments. Elderly customers or those with difficulty reading long text messages benefit significantly.
Context-driven preference: A YouGov study across 17 markets found that while text is still preferred overall, a notable share of users choose both text and audio depending on situation (YouGov survey).
Where voice notes make a difference
Voice messaging is especially useful when speaking feels more natural than typing—helping customers communicate in ways that fit their situation and needs.
Elderly customers – easier to listen than to read.
Field workers or drivers – easier to speak than to type while working.
Healthcare – patients can describe symptoms naturally by voice.
Hospitality and reservations – “Book a table for 7 pm” is faster to say than to navigate online calendar.
Customer support escalation – complex issues are often resolved more quickly with a voice exchange.
Voice notes don’t replace text. It complements it — giving customers the flexibility to communicate in the way that best suits their context.
AWS End User Messaging and WhatsApp
AWS End User Messaging is a managed AWS service that enables businesses to send and receive messages across multiple channels, including WhatsApp, SMS, MMS (US only), outbound voice, and push notifications.
When you use AWS End User Messaging for WhatsApp, you benefit from AWS’s global scale, resilience, and security. Inbound WhatsApp messages are automatically published to an Amazon SNS topic, enabling the integration with other AWS services such as Amazon SQS queues, AWS Lambda functions or Amazon Bedrock for downstream processing.
This flexibility is also what makes voice-to-voice messaging possible. Businesses can process inbound voice messages with Lambda, apply speech-to-text and text-to-speech services like Amazon Transcribe and Amazon Polly, or integrate third-party models such as Whisper through the AWS Marketplace for Amazon Bedrock.
git clone https://github.com/aws-samples/sample-whatsapp-voice-to-voice-messaging
cd sample-whatsapp-voice-to-voice-messaging
npm install
Before deploying, you’ll need to configure your WhatsApp phone number ID in the CDK context or parameters. The deployment will prompt you for this configuration, or you can set it in the cdk.json file. Once configured, deploy with:
cdk deploy
The CDK stack automatically provisions all required AWS resources including Lambda functions, SNS topics, S3 buckets, and IAM roles.
Clean up
To remove all resources and avoid ongoing charges:
cdk destroy
For detailed architecture diagrams, configuration options, and step-by-step setup instructions, visit the GitHub repository.
Conclusion
Customers are already using voice notes in their personal WhatsApp conversations. Bringing that same option into business communication makes customer interactions more natural, inclusive, and efficient.
With AWS End User Messaging and its WhatsApp channel, you can add voice alongside text without changing how customers connect to you. And with the sample CDK project, you can try it out today, experiment, and extend it for your own business needs.
There’s a new open-source plugin that snapshots your OpenClaw config, memory, and sessions to B2. It’s designed to be as simple as possible: Three fields to configure. Rollback from chat. Migrate to a new machine in one restart.
Let’s get into how and why you might want to use it.
OpenClaw keeps everything local. That’s great until it isn’t.
Your config, sessions, memory databases, hooks, cron jobs—everything that makes your OpenClaw instance yours lives on one machine with no built-in redundancy. Compaction can rewrite session transcripts and cause memory loss. A bad config edit or an accidental deletion means rebuilding from scratch: re-onboarding channels, re-pairing devices, re-teaching your agent who you are.
openclaw-b2-backup adds automatic encrypted backups to Backblaze B2 without changing how you use OpenClaw.
Three fields and you’re done
Setup is intentionally minimal:
openclaw plugins install openclaw-b2-backup
Then open ~/.openclaw/openclaw.json and add your B2 credentials to the entry the installer created:
Restart the gateway, and you’re done. Region is auto-detected from your application key. Encryption is on by default. The first backup runs at midnight, and then daily after that. You can change the schedule to weekly or any cron expression you like.
Free tier friendly: Backblaze B2 includes 10GB of free storage. A typical OpenClaw state directory is 50–500 MB, so even with 10 encrypted snapshots retained, you’ll comfortably stay within the free tier.
Backups that actually happen
The hardest part of any backup system is remembering to run it. This plugin takes care of that with multiple automatic triggers:
A daily cron job (configurable) runs a full incremental push at midnight.
Every time you shut down the gateway, a final push runs before exit—so you always have a snapshot of your latest state.
And, before compaction fires (the thing that rewrites your session transcripts and can cause memory loss), the plugin automatically pushes a snapshot. That last one is the one you’ll be most grateful for.
There’s a 5-minute debounce on the compaction trigger, so rapid-fire compactions don’t queue up a dozen pushes.
Rolling back from chat
The plugin registers a b2_rollback tool with your agent, which means you can manage backups conversationally. Just tell your agent:
“Show me my B2 backup snapshots”
And it’ll list all available snapshots with timestamps. To restore one:
“Roll back to the snapshot from before compaction”Before any restore, the plugin automatically creates a safety snapshot of your current state. Safety snapshots are stored separately and never auto-pruned, so you can always recover from a bad rollback. It’s an undo for your undo.
Moving to a new machine
This was one of the most requested use cases: Getting your entire OpenClaw setup onto a new machine without manually copying files and hoping you got everything.
Install the plugin on your new machine, add the same B2 credentials, and restart. The plugin detects the empty state directory, finds your existing snapshots in B2, and automatically restores the latest one. Same memory, same sessions, same config, same personality. No manual file copying.
openclaw plugins install openclaw-b2-backup
# Add your B2 config to openclaw.json
openclaw gateway restart
# Plugin detects empty state + existing snapshots → auto-restores latest
Security by default
Everything is AES-256-GCM encrypted before it leaves your machine. Each file gets a random salt and IV, so identical files produce different ciphertext. The encryption key is derived from your B2 application key via scrypt—no separate key to manage or lose.
Manifests (which contain only file paths and SHA-256 hashes) stay unencrypted so incremental diffing works regardless of encryption. Credentials and auth profiles are excluded from sync by design—secrets stay per-machine, and you re-auth on new machines.
Best practice: Use a B2 application key scoped to a single bucket for least-privilege access. The plugin works perfectly with bucket-scoped keys—region is auto-detected from the authorize response.
Zero external dependencies
The plugin has no external runtime dependencies beyond croner for scheduling. The B2 client is a hand-rolled AWS Signature V4 implementation using only node:crypto. No AWS SDK, no S3 library, no heavyweight dependencies to audit or keep updated.
It runs entirely inside the gateway process—no external scripts, no separate cron daemon, no stopping the gateway to take backups.
Get started
The plugin is open source (under the MIT license) and available now:
Sasha Levin has announced the release of the 6.12.76, 6.6.129, and 6.1.166 stable kernels. These releases
address a regression reported
by Peter Schneider; Levin said that an upgrade is only necessary for
those who have observed a build failure with the 6.12.75, 6.6.128, or
6.1.165 kernels.
The multi-generational LRU (MGLRU) is an
alternative memory-management algorithm that was merged for the 6.1 kernel
in late 2022. It brought a promise of much-improved performance and
simplified code. Since then, though, progress on MGLRU has stalled, and it
still is not enabled on many systems. As the 2026 Linux Storage,
Filesystem, Memory-Management and BPF Summit (LSFMM+BPF) approaches,
several memory-management developers have indicated a desire to talk about
the future of MGLRU. While some developers are looking for ways to improve
the subsystem, another has called for it to be removed entirely.
It satisfies compliance requirements for runtime-related vulnerabilities.
DAST catches vulnerabilities in the running web application, yielding findings that may be missed in static code testing.
It is security-drivenwith little overhead in configuration/maintenance from development or application teams.
Due to the nature of web apps powering mission-critical operations – hyperscaled of course by AI protocols that automate key processes within these apps – continuous DAST is essential to identifying and remediating potential weaknesses that could quickly lead to costly data breaches.
Compliance requirements
DAST helps satisfy multiple compliance requirements by simulating real-world attacks so it can test a running application for vulnerabilities.. While DAST alone doesn’t make you compliant, it supports key controls in many security standards and regulations. Get to know 7 of today’s top standards and frameworks, see which requirements they satisfy, and learn how DAST helps secure the following:
PCI DSS
Payment Card Industry Data Security Standard(PCI DSS) is the global security standard for any organization that stores, processes, or transmits payment-card data. DAST directly supports PCI compliance by performing vulnerability scans against live web apps.
Requirements satisfied:
Requirement 6.1 & 6.2: Identifying and addressing vulnerabilities.
Requirement 6.6: All public-facing web applications must be either:
Protected with application-layer firewall (WAF), or
Tested for vulnerabilities (e.g., via DAST) at least annually.
OWASP Top Ten
While the Open Worldwide Application Security Project (OWASP) is not a compliance framework, the nonprofit organization is often referenced by industry and regulatory standards.
Requirements satisfied:
DAST tools are often tested against OWASP Top 10 vulnerabilities (e.g., XSS, SQLi, SSRF).
HIPAA
The Health Insurance Portability and Accountability Act (HIPAA) sets national standards for protecting electronic protected health information (ePHI). DAST supports risk assessment by identifying live vulnerabilities with the potential to expose such information.
Requirements satisfied:
Security Rule (45 CFR § 164.308 & § 164.312):
Requires organizations to perform regular risk assessments.
Includes application-level vulnerabilities as part of overall system security.
ISO/IEC 27001
ISO/International Electrotechnical Commission (ISO/IEC) isthe international standard that specifies requirements for an information security management system (ISMS). DAST helps fulfill this requirement by scanning running applications for known and exploitable vulnerabilities.
Requirements satisfied:
Annex A.12.6.1: Management of technical vulnerabilities – Requires timely detection and remediation of vulnerabilities.
NIST SP 800-53/800-171
The National Institute of Standards and Technology (NIST) is a U.S. federal agency that develops measurement science, standards, and tech to boost innovation and economic security. DAST can be used to meet these technical controls.
Requirements satisfied:
RA-5 (vulnerability scanning): Requires scanning of systems and applications.
SI-2 (faw remediation): Identify, report, and fix flaws in software.
SOC 2
System and Organization Controls 2 (SOC2) isan independent attestation report (from a licensed CPA firm) that evaluates whether a service organization’s controls are suitably designed. DAST contributes evidence for audit logs and control effectiveness over time.
Requirements satisfied:
Under the “Security” Trust Services Criteria, particularly:
CC4.1: Monitor infrastructure for new threats.
CC7.1/CC7.2: Detect and mitigate vulnerabilities.
GDPR
General Data Protection Regulation (GDPR) harmonizes privacy rules across the EUand sets requirements for how organizations collect, use, share, and protect personal data. DAST can be part of regular security testing under GDPR, especially if the app processes personal data.
Requirements satisfied:
Article 32 – Security of Processing:
Organizations must ensure the ongoing confidentiality, integrity, availability of systems.
Requires regular testing and evaluation of security measures.
Missed findings
Static application security testing (SAST) tools are effective at flagging insecure values on their own, but they often miss the broader application context needed to assess whether those values actually introduce risk. Here are some examples of findings that can be overlooked:
Forced browsing
Forced browsing (also called insecure direct object reference or unauthorized resource access) occurs when:
A user can manually access restricted resources (files, endpoints, or actions) by guessing or modifying a URL.
There are missing access controls or authorization checks.
Example: A user modifies a URL
https://example.com/admin/settings
Even though they’re not an admin, the app still serves the page because it lacks proper access controls.
SAST struggles to detect these findings due to:
Lack of visibility into runtime access control
SAST scans source code, but can’t simulate user roles or sessions.
It doesn’t know who should or shouldn’t be able to access a specific path.
Abstracted access control logic
Authorization might be handled via middleware, annotations, config files, or external services (e.g., OAuth).
SAST often can’t follow the full enforcement logic, especially if it’s custom or dynamic.
Lack of awareness around routing and resource exposure
SAST doesn’t map which endpoints exist versus which are intended to be public.
It can’t verify which files/resources are accessible through URLs.
Out-of-band (OOB) cross-site scripting (XSS)
Out-of-band cross-site-scripting OOB XSS (a subtype of stored or blind XSS) occurs when:
A malicious script is injected into an application (e.g., a form, comment, or field).
The script doesn’t execute immediately but instead fires later, often:
In a different user’s browser (e.g., an admin viewing logs).
In an email client (e.g., via notification messages).
In a third-party system or admin dashboard.
These attacks are asynchronous and context-shifted, meaning they don’t happen in the direct request-response flow. SAST struggles to detect these findings due to:
Missing runtime context: SAST analyzes source code statically, line by line, without executing it. It doesn’t track:
Where the injected payload ends up.
How or where it’s later rendered.
Whether it’s rendered in a dangerous context (HTML, JS, email, etc.).
Visibility is limited to code flow: SAST typically can’t follow data across storage layers or external systems. OOB XSS often spans:
User-submitted input → stored in DB.
Later retrieved → rendered in admin UI or email.
Unable to observe execution: The XSS payload doesn’t fire in the original request, so SAST has no way to “see” the exploit being triggered because it doesn’t execute code.
Web config findings
Settings defined in the web config file can pose challenges for SAST tools. Depending on the tooling, these files may not be properly parsed, potentially causing the tool to miss important findings due to a lack of contextual understanding, such as:
Custom error handling depends on deployment mode
<customErrors mode="RemoteOnly" />
⠀ ✔ Looks fine in static analysis; it shows friendly errors to remote users.
✖ Contextual issue: If the app is misconfigured to treat all users as local, then stack traces are exposed even with this setting.
SSL enforcement logic in code, not in config.
<rewrite>
<!-- Missing rule for HTTPS redirection -->
</rewrite>
⠀ ✔ SAST flags the absence of HTTPS redirection in web.config, which is a valid finding.
✖ Contextual issue: If HTTPS redirection is handled in middleware or at a reverse proxy (like NGINX or Azure App Gateway), then this isn’t actually a security risk. SAST can’t always know that.
Authentication mode
<authentication mode="None" />
⠀ ✔ SAST will likely flag this as a critical issue.
✖ Contextual issue: If the app is a microservice behind an API gateway that handles auth, this may be acceptable. A SAST tool unaware of deployment architecture may raise false positives.
Debug enabled in a non-prod environment
<compilation debug="true" />
⠀ ✔ Flagged by SAST, correctly so in most cases.
✖ Contextual issue: If this web.config is only used in a staging or development slot, it might be intentional and not a production risk.
Authorization settings ignored in custom pipelines
✖ Contextual issue: If a custom authentication mechanism bypasses ASP.NET authorization modules, this setting may be ineffective, but a SAST tool won’t see that unless it’s deeply integrated with the entire codebase.
Developer overhead
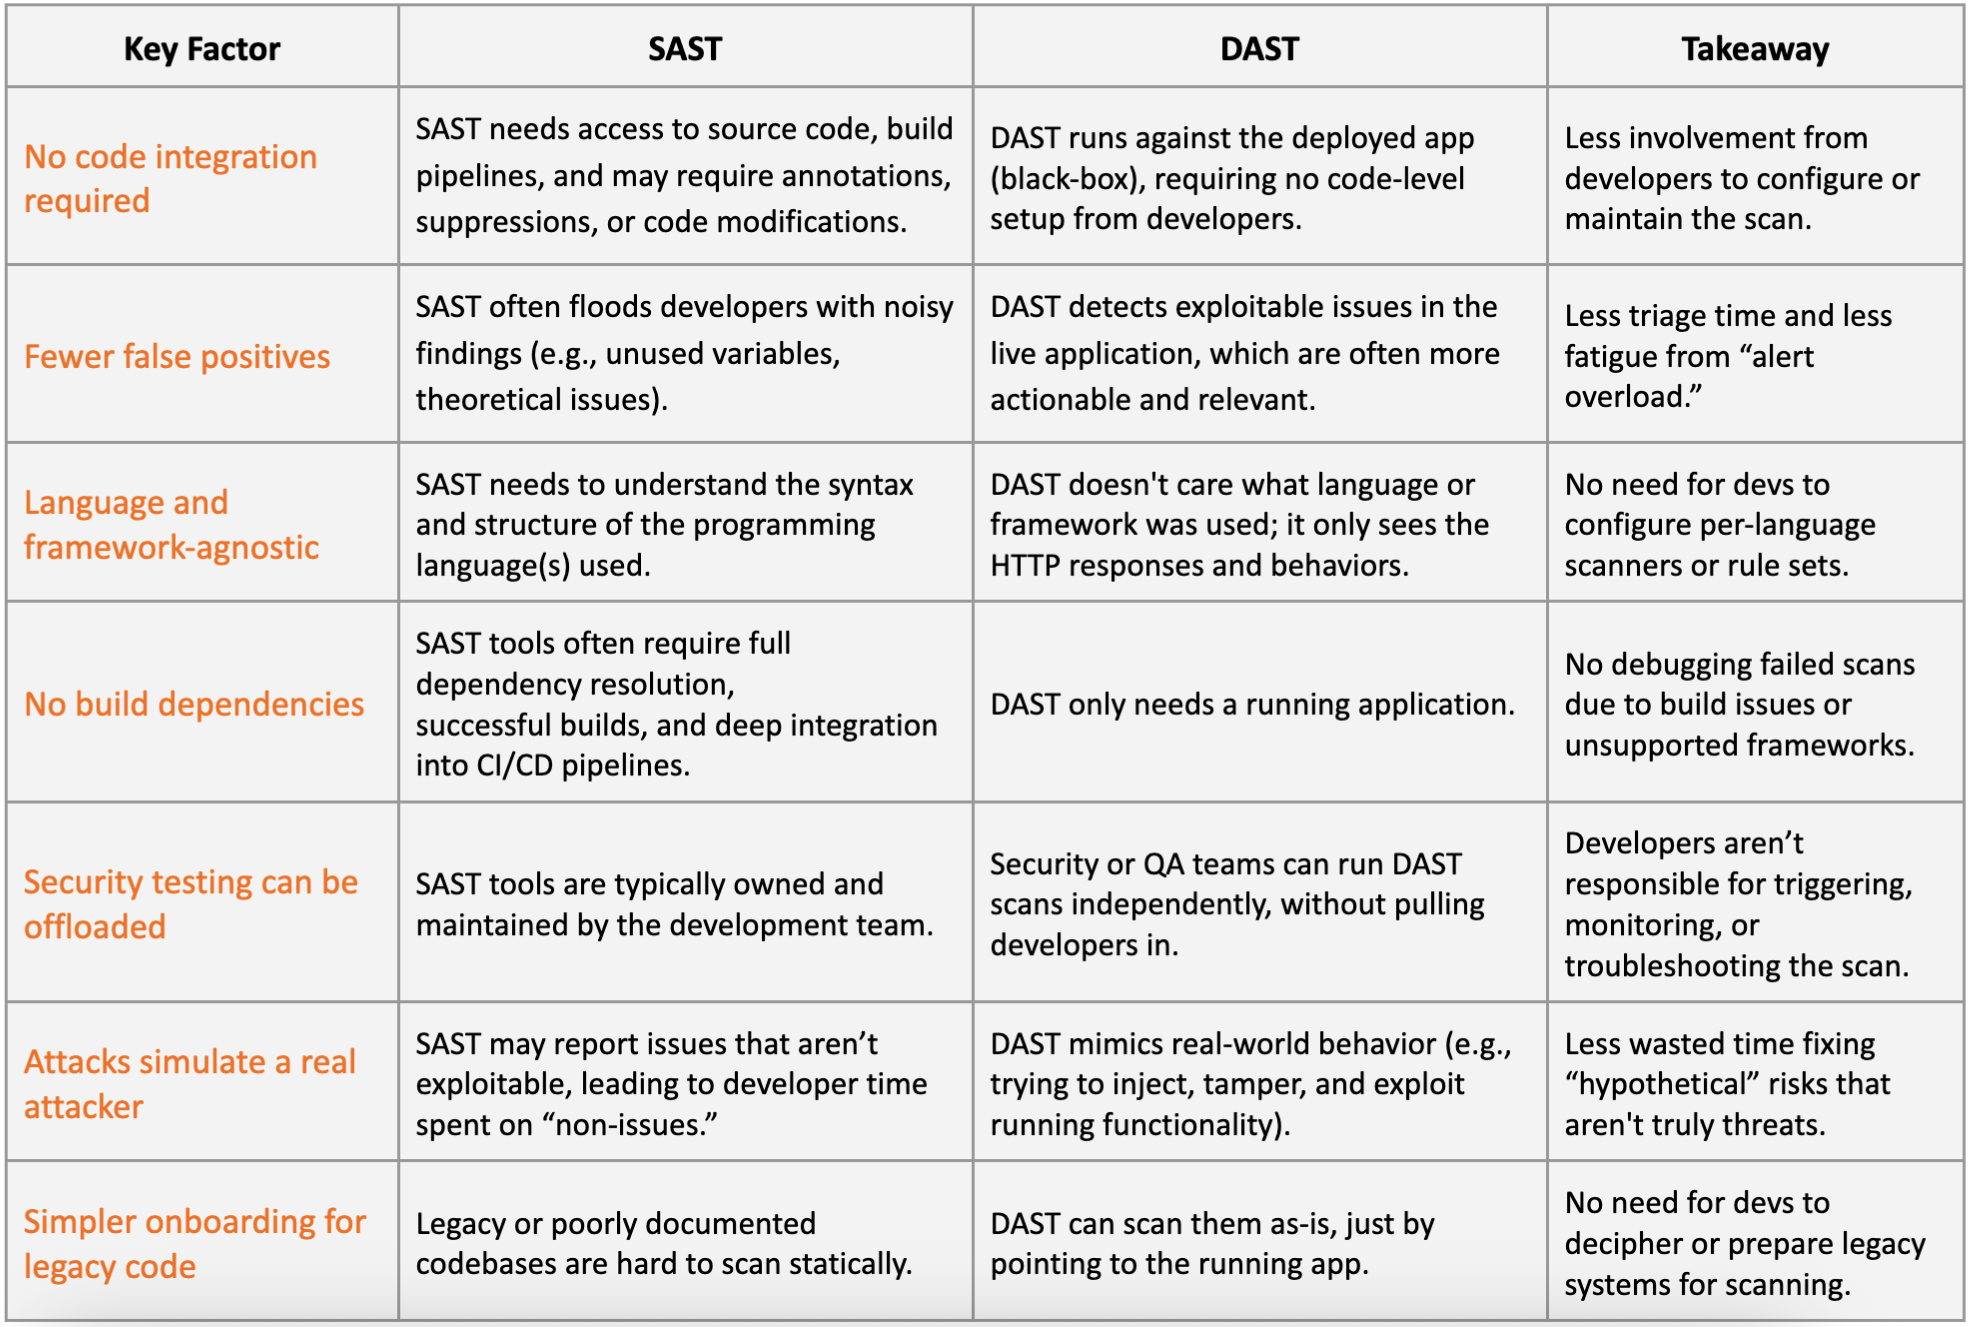
For organizations seeking to minimize developer burden, DAST is frequently the preferred option over SAST. DAST processes evolve alongside your web applications, continuing to scan them so that your business can promptly identify and remediate emerging issues. Let’s finish by taking a look at a range of underlying dynamics that make DAST an easy decision for developers looking to fortify application security – table below.
You’ve likely seen this support ticket countless times: a user’s Internet connection that worked just fine a moment ago for Slack and DNS lookups is suddenly hung the moment they attempt a large file upload, join a video call, or initiate an SSH session. The culprit isn’t usually a bandwidth shortage or service outage issue, it is the “PMTUD Black Hole” — a frustration that occurs when packets are too large for a specific network path, but the network fails to communicate that limit back to the sender. This situation often happens when you’re locked into using networks you do not manage or vendors with maximum transmission unit (MTU) restrictions, and you have no means to address the problem.
Today, we are moving past these legacy networking constraints. By implementing Path MTU Discovery (PMTUD), the Cloudflare One Client has shifted from a passive observer to an active participant in path discovery.
Dynamic Path MTU Discovery allows the client to intelligently and dynamically adjust to the optimal packet size for most network paths using MTUs above 1281 bytes. This ensures that a user’s connection remains stable, whether they are on a high-speed corporate backbone or a restrictive cellular network.
The “modern security meets legacy infrastructure” challenge
To understand the solution, we have to look at how modern security protocols interact with the diversity of global Internet infrastructure. The MTU represents the largest data packet size a device can send over a network without fragmentation: typically 1500 bytes for standard Ethernet.
As the Cloudflare One client has evolved to support modern enterprise-grade requirements (such as FIPS 140-2 compliance), the amount of metadata and encryption overhead within each packet has naturally increased. This is a deliberate choice to ensure our users have the highest level of protection available today.
However, much of the world’s Internet infrastructure was built decades ago with a rigid expectation of 1500-byte packets. On specialized networks like LTE/5G, satellite links, or public safety networks like FirstNet, the actual available space for data is often lower than the standard. When a secure, encrypted packet hits an older router with a lower limit (e.g., 1300 bytes), that router should ideally send an Internet Control Message Protocol (ICMP) message stating “Destination Unreachable” back to the sender to request a smaller size.
But that doesn’t always happen. The “Black Hole” occurs when firewalls or middleboxes silently drop those ICMP feedback messages. Without this feedback, the sender keeps trying to send large packets that never arrive, and the application simply waits in a “zombie” state until the connection eventually times out.
Instead of waiting for an error message that might never come, the client proactively sends encrypted packets of varying sizes to the Cloudflare edge. This probe tests MTUs from the upper bound of the supported MTU range to the midpoint, until the client narrows down to the exact MTU to match. This is a sophisticated, non-disruptive handshake happening in the background. If the Cloudflare edge receives a specific-sized probe, it acknowledges it; if a probe is lost, the client instantly knows the precise capacity of that specific network segment.
The client then dynamically resizes its virtual interface MTU on the fly, by periodically validating the capacity of the path that we established at connection onset. This ensures that if, for example, a user moves from a 1500-MTU Wi-Fi network at a station to a 1300-MTU cellular backhaul in the field, the transition is seamless. The application session remains uninterrupted because the client has already negotiated the best possible path for those secure packets.
Real-world impact, from first responders to hybrid workers
This technical shift has profound implications for mission-critical connectivity. Consider the reliability needs of a first responder using a vehicle-mounted router. These systems often navigate complex NAT-traversal and priority-routing layers that aggressively shrink the available MTU. Without PMTUD, critical software like Computer Aided Dispatch (CAD) systems may experience frequent disconnects during tower handoffs or signal fluctuations. By using active discovery, the Cloudflare One Client maintains a sticky connection that shields the application from the underlying network volatility.
This same logic applies to the global hybrid workforce. A road warrior working from a hotel in a different country often encounters legacy middleboxes and complex double-NAT environments. Instead of choppy video calls and stalled file transfers, the client identifies the bottleneck in seconds and optimizes the packet flow — before the user even notices a change.
Get PMTUD for your devices
Anyone using the Cloudflare One Client with the MASQUE protocol can try Path MTU Discovery now for free. Use our detailed documentation to get started routing traffic through the Cloudflare edge with the speed and stability of PMTUD on your Windows, macOS, and Linux devices.
If you are new to Cloudflare One, you too can start protecting your first 50 users for free. Simply create an account, download theCloudflare One Client, and follow ouronboarding guide to experience a faster, more stable connection for your entire team.
Три минути. Толкова е времето между гласуванията на първо и второ четене на законопроект, приет с пълно мнозинство от 186 депутати от всички парламентарни групи (плюс четирима независими), присъстващи на заседанието на Народното събрание на 19 февруари 2026 г. Без дискусии, без експертни становища, без оценка на въздействието. Гласуването на първо четене е в 10:51, а на второ – съответно в 10:54.
Кой е нормативният акт, променен с такова забележително единодушие?
Става въпрос за Закона за закрила на детето (ЗЗД). Конкретно – за т.нар. регистър на педофилите, приет през лятото на 2023 г. по предложение на „Възраждане“. Отново „Възраждане“ инициира и гласуваното на 19 февруари изменение. С него част от регистъра става публична. По-специално, „три имена на извършителя, дата на раждане, постоянен и настоящ адрес, вид престъпление и размер на наказанието“, а за чужденците се включват и „данните за държавите по произход“.
Това нововъведение може да има последствия, отиващи твърде далеч – не само за извършителите, а и за някои от жертвите им, но също така и за цялото общество. Преди да се спрем върху потенциалното му въздействие обаче, нека припомним контекста, в който то беше прието.
Не консенсус, а поддаване на натиск
Гласуването на промените в ЗЗД става на фона на политическата употреба на една трагедия – смъртта на шестима души, между които и непълнолетно момче, в хижа „Петрохан“ и край връх Околчица. Още преди да стане ясно колко са мъртвите, случаят беше свързан с „педофилията“ и „сектите“ – токсични теми, особено когато са в комбинация, а отговорността беше хвърлена върху ПП–ДБ. Заради споразумение без правна сила, подписано от министър, чиято партия вече дори не е част от тази коалиция.
Етикетът „педофилия“ е прикрепен към трагедията на основата на твърдения от страна на един човек, който казва, че е имал интимни отношения с лидера на групата, когато е бил на 15 и повече години, и на подадени сигнали от роднини на дете – опасенията, изразени в тях, не са потвърдени. Дори да се окажат верни, няма никакви данни някой от ПП–ДБ да е знаел за това.
Под привидното единство при гласуването на промените в ЗЗД се открояват три вида парламентарни групи.
Първите („Възраждане“, ИТН и ДПС – Ново начало) активно призовават „регистърът на педофилите“ да стане публичен. Вторите (ПП–ДБ) се снишават, защото и без това без вина вече са обвинени в педофилия. Третите (останалите) са пасивни наблюдатели – било защото са печеливши от ситуацията (основно ГЕРБ), било за да не се набутват между точно тези токсични шамари.
Интересен детайл е, че макар законопроектът да е на „Възраждане“, представителите на партията са обрани в изказа си. Те изтъкват преди всичко необходимостта да бъдат защитени децата, позовавайки се на информация за различни форми на сексуални престъпления срещу малолетни и непълнолетни. Докладчикът Георги Хрисимиров посочва и статистически данни, показващи увеличаване на случаите на трафик на деца. Последното е отчасти подвеждащо, защото сексуалната експлоатация е само една от формите на трафик – наред с трудовата експлоатация, просията или търговията с органи.
За разлика от Хрисимиров, Тошко Йорданов (ИТН), който взема думата още преди депутатът от „Възраждане“ да е представил законопроекта, е неудържим. Той многократно използва думи, производни от „педофилия“, а следните словосъчетания – по няколко пъти: „педофилска секта“ (три пъти, два от които в съчетание с „петроханската“) и „ламата педофил“ (три пъти). В този словесен коктейл Йорданов 12 пъти споменава абревиатурата НПО в негативен контекст (едно от споменаванията гласи „педофилското НПО“), а ПП–ДБ, в същия контекст – 6 пъти. Без да броим споменаването на множество настоящи и бивши представители на коалицията и политици, асоциирани с нея.
И Хамид Хамид от ДПС – Ново начало споменава „педофилски НПО-та“. За разлика от Тошко Йорданов, който обвинява хора, организации и партии в прав текст, Хамид прави намеци като „има парламентарни групи, които се хвърлят на амбразурата да защитават педофилските прояви“. Когато заявява: „Макар и служебно, педофилите проникнаха в правителството на Република България“, председателката на Народното събрание Рая Назарян го съветва да се въздържа „от подобни квалификации“.
Ден по-рано впрочем, на 18 февруари, Хамид предложи възрастта на съгласие, която според Наказателния кодекс е 14 години, да се вдигне на 16 – отново без оценка на въздействието. Това беше прието, засега само на първо четене. Ако мине и на второ, 18-годишните, които са в сексуална връзка с 15-годишни, вече ще са престъпници и ще могат да влязат в „регистъра на педофилите“.
Възможни последствия от публичния регистър
На пръв поглед основанията за промяната в ЗЗД изглеждат благовидни. Да си представим обаче, че публичният регистър вече е факт, и да проиграем няколко възможни хипотези:
Първа хипотеза. Благодарение на регистъра живеещите в един блок разбират, че техен съсед е осъждан за педофилия. За да предпазят децата си, те го принуждават да напусне своя апартамент. Съседите си отдъхват. Но този човек не може да си намери жилище другаде, защото при всеки опит престъплението, за което е осъден, излиза наяве. Ако не иска да остане бездомен, ще му се наложи да заживее някъде, без да се регистрира адресно. За новите му съседи регистърът ще е безполезен, защото няма да знаят кой е този човек. Може да предположим, че немалко от включените в регистъра биха постъпили именно така, за да могат изобщо да живеят някъде.
Втора хипотеза. Случай на сексуално престъпление срещу дете става медийно известен. След излежаване на присъдата си извършителят излиза на свобода. Възмутени граждани решават да вземат нещата в свои ръце. От регистъра разбират къде живее той. Причакват го и го подлагат на линч, в резултат на който човекът умира. А възмутените граждани стават подсъдими за убийство.
Трета хипотеза. Осъден за сексуално престъпление срещу дете не живее нито на постоянния, нито на настоящия си адрес. Но хората, които живеят на тези адреси, стават непрекъснато обект на тормоз и агресия от страна на „борци с педофилията“. Макар да не са извършили нищо нередно, а някои от тях може дори да са жертви на осъдения.
Четвърта хипотеза. Баща е осъден, защото е насилвал сексуално детето си. Понеже бащата е в регистъра, познатите на семейството и на детето могат да се досетят, че именно то е жертвата. Така, вместо детето да се възстановява психически и да намери сили да продължи напред, публичността на посегателството прибавя нова травма към вече съществуващата.
Пета хипотеза. Лице със сексуални предпочитания към деца и много пари има идея как да разреши проблема с намирането на жилище за осъдените за педофилия, или поне на някои от тях. Построява сграда, в която се заселват само такива като него. Разбира се, под сурдинка. Обитателите на сградата заживяват като сплотена група, влияейки се един от друг, вместо да са в среда, която ги стимулира да потискат склонностите си. Организират си партита, на които присъстват малолетни. Така, вместо децата да са по-защитени, стават по-уязвими.
Шеста хипотеза. Извършители на сексуални престъпления срещу деца, които имат дебели връзки и/или са злоупотребявали с деца, за които на обществото не му пука особено, правят всичко по силите си да не бъдат осъдени. Съответно регистърът не се отнася за тях.
Пардон, последното не е хипотеза, а факт. Сещате ли се за протестантския пастор, за когото има данни, че е насилвал поне 14 деца от ромския квартал „Надежда“ в Сливен? Той е подсъдим от почти три години, но досега близо 30 съдии са подали отвод по делото. И няма кой да го осъди. А учителката от Каблешково – повече от година след като случаят стана публичен, няма информация за движението по разследването срещу нея. Въпреки че казусът беше прехвърлен на варненската прокуратура, след като бургаската с нищо не показа, че защитава интересите на детето. Много случаи на сексуална злоупотреба с деца пък потъват, без изобщо да станат публично известни.
С инициирането на публичен „регистър на педофилите“ „Възраждане“ не открива топлата вода. Подобни практики съществуват например и в САЩ. В някои страни от Западна Европа подходът е по-скоро противоположен – дори за престъплението да се съобщава, не се споменава името както на жертвата (или жертвите), така и на извършителя. А ако името на престъпника е било известно, има процедура то да бъде „забравено“ в интернет. На тази тема е посветен анализ (на английски език) в YouTube канала Type Ashton.
Основанията за премълчаването на самоличността на извършителя са поне две. Първо, след като е изтърпял наказанието си, се очаква той да има възможност да се реинтегрира в обществото. Всеки, който не е осъден на доживотен затвор, би следвало да има този шанс.
Второ, когато извършителят не е известен, това намалява риска да се появят негови подражатели. Има немалко случаи на хора, които стават престъпници, защото са се вдъхновили от други престъпници, добили популярност в публичното пространство.
Що се отнася до „възпиращата“ функция на публичния регистър, има предостатъчно данни, че тежестта на едно наказание няма особена превантивна функция. Щом дори перспективата за смъртна присъда не спира някои хора да извършват определени престъпления, рискът от публично опозоряване едва ли би имал по-сериозен ефект за тях. Да не забравяме, че Щатите може да си имат публични регистри, но си имат и досиетата „Епстийн“.
В България обаче акцентът пада върху тежестта на наказанията, а не върху превенцията. Ако някой има сексуална склонност към деца, той или тя може да не е в състояние да я преодолее, но е възможно да се научи да я контролира, ако получи съответната подкрепа. И в резултат на това да не злоупотребява с деца. Както един алкохолик не престава да бъде такъв, но може да спре да пие.
В немската документална поредица Die Frage например се представя историята (на немски език, но са налични и български субтитри) на интимна двойка мъж и жена. Те са част от група за взаимопомощ на педофили, обединени от каузата, че не искат да стават извършители, и получават психологическа подкрепа.
Друга форма на превенция, която в България не се радва на одобрение, е сексуалното образование. Колкото по-рано едно дете знае кое отношение към тялото му е в реда на нещата, кое не и как да реагира, ако допустимите граници бъдат прекрачени, толкова по-способно ще е то да разпознава сексуалната злоупотреба. И съответно да се предпазва от нея.
Работата с родителите е също много важна с оглед на превенцията. Защото някои от тях отказват да повярват, че детето им е било сексуално насилвано, особено ако извършителят е познат на семейството и то има доверие в него. Да не говорим, че има родители, които знаят, но си затварят очите. Особено ако извършителят е другият родител (кръвен или доведен) или техен интимен партньор.
Когато една тема е табу, представите за нея са мъгляви и безформени. Така е с педофилията. За да можем ефективно да се предпазим от нещо обаче, на първо място трябва да знаем какво е то. Ала какво разбираме под педофилия?
Първо, дали е склонност, или постъпка? Според Световната здравна организация (СЗО) е влечение. В едно демократично общество човек не може да бъде осъден единствено защото има някаква склонност – престъпление е само ако направиш нещо (или не направиш, а е трябвало).
Второ, на каква възраст трябва да е едно дете, за да става дума за педофилия? Според СЗО педофилията е влечение към деца в предпубертетна или ранна пубертетна възраст. В българския Наказателен кодекс думата „педофилия“ не се споменава, но са забранени сексуалните контакти с деца под 14-годишна възраст. Над 14 са разрешени, освен при определени случаи, например когато тийнейджърите са в зависима позиция спрямо извършителя. Регистърът на случаите на педофилия обаче включва извършителите на сексуални престъпления срещу лица до 18 години. В широк смисъл думата се използва за сексуални контакти с лица, ненавършили възрастта за съгласие, независимо каква е тя.
Трето, трябва ли да има някаква възрастова разлика между извършителя и детето, за да можем да говорим за педофилия? Според здравия разум – да, според българското законодателство – не. Ако 18-годишно момче е правило секс с 13-годишно момиче, защото момичето го е излъгало, че е на 16, момчето може да бъде осъдено. И да влезе в регистъра на педофилите.
50-годишен човек обаче, който е във връзка с 14-годишно дете по взаимно съгласие, няма да влезе в регистъра. В Германия например възрастта за съгласие е също 14 години, но човек, имащ сексуални отношения с тийнейджър между 14 и 16 години, трябва да е най-много на 21. В България, вместо да се помисли за въвеждане на подобна възрастова разлика, директно се върви към увеличаване на възрастта за съгласие. За да се създадат „служебно“ още повече престъпници и да има с какво да се пълни регистърът.
Но може би целта е да нямаме общо споделено разбиране за педофилията, а да я възприемаме като аморфно плашило.
Така тя ще продължи успешно да се използва като средство за натиск, за опозоряване на политически противници и на НПО-тата. Дори въпросните партии, политици и неправителственият сектор като цяло да нямат нищо общо с педофилията и със сексуалните престъпления срещу малолетни и непълнолетни.
А който си позволи да изрази критично становище, трябва да е готов да поеме риска да му лепнат етикета „защитник на педофилията“. И все пак някой трябва да го прави, защото иначе съвсем ще затънем в блатото на популизма – със съдействието на партиите, които уж са демократични, но ги е грижа за оцеляването си повече, отколкото за демократичните ценности.
И няма кой да повдигне въпроса: в европейско общество ли искаме да живеем, което цени хуманизма, или в общество на позорни стълбове и линчове?
В крайна сметка „Възраждане“, които също се борят за политическото си оцеляване на фона на новия политически проект на Румен Радев, победиха без бой. За трети път, след като през 2023 г. предложиха „регистъра на педофилите“ и той беше приет, а година по-късно инициираха промените в Закона за предучилищното и училищното образование, с които беше забранено говоренето по теми, свързани с ЛГБТИ. А ПП–ДБ, колкото и да се снишават, са в губеща позиция.
Британците казват, че любопитството убива котката. Може да добавим, че популизмът убива политиката.
Да проектираш сграда, която да остане в живота на няколко поколения, да оформяш физиономичността на града е културен жест, към който архитектите от всички времена са се отнасяли с респект. След тях обаче идват грижата и разбирането на културните историци, които интерпретират контекста.
Теодор Караколев е сред най-разпознаваемите изследователи на българската архитектура между двете световни войни и съосновател на Фондация „Български архитектурен модернизъм“. Фондацията изследва образци на архитектурата и изкуството в периода между 20-те и 40-те години на миналия век, организира изложби и лекции, поддържа една от най-големите онлайн общности, интересуващи се от архитектурно наследство.
Журналист и лектор в множество инициативи, включително и архитектурни обиколки, с деликатното си академично присъствие Тео Караколев предлага мултидисциплинарен подход. Не просто да архивира, а да напомня, че сме част от процес, от непрекъсната трансформация на търсенията и контекста – това е мисията на „Български архитектурен модернизъм“.
В началото много мислех върху това колко голяма част от архитектурната история акцентираше върху сградите. Хората ги нямаше – какви са били, какво са правили, каква е връзката между човека и сградата. А интериорите също са част от ежедневието ни. На връщане към къщи може да избереш четири-пет маршрута. Но влезеш ли, имаш само едно стълбище, понякога го ползваш през целия си живот. Ако си израснал в някоя сграда, ще ти е трудно да я видиш с нови очи. Тя е тривиална част от теб, несъзнавано усещане, което те формира. Затова за мен е важно да покажем на хората, че това, което обитават, е всъщност красиво, достойно.
Никой не си прави илюзията, че градовете ни не са опърпани, недобре поддържани, „но не са безвъзвратно грозни“, настоява Тео Караколев.
Важно е да знаем, че средата ни има стойност. Това, което се нуждае от ремонт, може да бъде поправено. Градската ни среда има стойност. Това особено силно важи за по-малките населени места, където хората са се затворили.
А всичко започва именно от ентусиасткото отстояване на вярата, че информацията трябва да бъде достъпна. И от една страница в социалните мрежи. Дипломната работа на Васил Макаринов в Нов български университет е свързана точно с архитектурата на модернизма и след защитата той решава да публикува събраните материали. Годината е 2013-та и страницата предизвиква неподправен интерес. Тео Караколев му изпраща информация за сгради от Сливен – така се запознават и бързо откриват, че искат да работят заедно. Извън дигиталното пространство и двамата продължават изследователската си дейност и надграждат с лекции, изложби и събития на живо за изкушени от темата непрофесионалисти.
Освен изследователско ровене из архиви и общински документи, работата на Васил Макаринов (за съжаление, напуснал ни твърде рано) и Теодор Караколев е да проследяват историята на множество малки сгради, да идентифицират архитекти, да анализират стилови особености. Те систематично документират и описват десетки малки обществени сгради, училища, читалища и къщи на заможни семейства в градове като Пловдив, Варна, Бургас, Стара Загора, Ямбол, Казанлък.
Това, което „Български архитектурен модернизъм“ като платформа успява да постигне, е повишаване на обществената чувствителност към опазването на ценни сгради.
Тео Караколев е завършил изкуствознание в НБУ, докторант е в направление „Изобразителни изкуства“ към АМТИИ, но още като тийнейджър е заинтригуван от фотографията, снима кадри, които са на ръба на абстракцията, имат ритъм и семпла конструкция, ясни форми, основно черно-бяло или монохромно. Впоследствие открива, че същите неща търси и в архитектурата. Едва ли е случаен интересът му към ар деко и функционализма, както и последователното проучване на сгради образци.
Историята на изкуството и историята на архитектурата са свързани, разделението, което съществува в България, го няма на други места. Това, което ние се опитваме да правим, е изкуствоведски поглед към архитектурата.
Разделянето на стилове и периоди улеснява научния разказ за историята, но унищожава човека, твореца. Всеки е конкретна индивидуалност със своя собствена душевност. Твори в конкретен период – барок, ренесанс, модернизъм – и ако бъде поставен в съответния период, ще създаде различни неща в духа на своето време. Но винаги ще бъде себе си.
Така че аз харесвам определен тип творци, а не течения. Предпочитам такива, които не са толкова разказвателни и директни в посланието си.
Тео Караколев с основание акцентира върху факта, че няма направления, които да се ограничават само до конкретни послания, но има творци, които настояват върху разделението на добро и лошо, на приемливо и неприемливо, на допустимо и недопустимо.
Предпочитам тези, които ми оставят място за мислене, задават въпроси и провокират. Наскоро отново разглеждах постоянната експозиция на Националната галерия. И ето например Иван Милев – той е представен там със свои обичайни сюжети: жени със забрадки, задушници, погребения. Аз не съм сигурен какво трябва да мислим за тях. Дали те са тъжни, какво става, продължава ли животът, трябва ли да го надмогнем? Няма директна трагедия. А те обзема усещането, че и друг преживява същото, през което и ти минаваш. Изкуството е това, за което можеш да се хванеш.
При Златю Бояджиев например любим ми е периодът непосредствено преди инсулта му. Там той е най-прецизен, най-конкретен в рисунъка си. Има няколко сюжета с овчари, хора на нивата – по същия начин животът изглежда труден, но има надежда. В трудността има смисъл.
Търсенията на Теодор Караколев са категорично отвъд лесните отговори. В дълбочината и непознаваемостта на изкуството. Там, където има живот, а не опит да се документира действителността или да се изведе лесно послание.
В годините, в които се е налагало да чете задължителна литература в училище, Тео Караколев си е спестявал колкото може от програмата, за да освободи пространство за собствените си интереси. Днес не го нарича бунтарство, но се съгласява да го определим като независимост. Това е времето, в което открива Гогол и Достоевски.
Конкретно в рецепцията на архитектурата днес той наблюдава консервативна реакция, която призовава за връщане към академичното. В последните години в различни среди става популярна критиката на модернизма и противопоставянето ѝ на европейската архитектура от времето до XIX век. Подобен прочит е повърхностен, създава фалшива представа и не отчита колко прогресивни са били конкретни артисти за времето си. Парадоксално е например приемането за академичен пример на „сецесиона – течение, което свързваме с неговата пищност, с неизговорените желания, но и с критиката му към академизма“.
И преди, и сега архитектурата бива използвана за политически битки.
Дали обаче изкуството преднамерено не улавя бъдното? Според Тео Караколев ние сами конструираме подобни очаквания. Историята на изкуствата е пълноводно течение и ние избираме върху кое да акцентираме, какво да разкажем. Невинаги знаем кой е бил по-влиятелен в собственото си време. Не можем да сме сигурни, че конкретен артист провижда идващо събитие, защото около него има още стотина, които улавят други неща.
Ето например филмът от 1920 г. „Кабинетът на доктор Калигари“, който е интерпретиран като предсказване за идването на Хитлер заради сляпото доверие, хипнозите, сомнамбулизма. Но не е ли твърде лесно да се намери тази връзка, когато събитието вече се е случило? Всяко произведение от този период показва несигурността, алтернативните търсения, несъзнаваното.
По-глобално погледнато, не вярвам, че историята има предначертан предварително път. Върху общия поток силно влияят отделни хора или групи от хора.
Именно такава група успява да генерира около себе си „Българският архитектурен модернизъм“. Самият Тео споделя, че има нужда от това да вярва в гражданската енергия, структурирана в отделни миниобщества.
Чисто исторически има периоди на концентрация на история. В България в годините малко преди влизането в Европейския съюз досега сякаш имаше някакъв що-годе консенсус какво правим и накъде се движим. Сега сме в друг момент. Но отвъд злободневното аз мисля, че конкретният човек може да влияе силно, макар и върху малък кръг хора. И това е гражданското общество – съществуването на голям брой хора, които са активни. Ако обществото е здраво, то ще намери реакция срещу тоталитарните държави. Може би затова Германия успява да се възроди след Хитлер. Въпреки травмата.
Основното за мен е много хора да вярват, че могат да променят нещата. Това е силата на гражданското общество.
Теодор Караколев открива собствения си път. И днес, докато се разхожда в Стария град на Пловдив или по тепетата, в кварталите и край реката, обича понякога да е сам.
Понякога предпочита разходките из непознати градове пред контролираната музейна среда. Но истински си почива в планината. Въпреки заниманията си със скално катерене се определя скромно като планинар.
Градовете ми дават цивилизационно преживяване, а планината е мястото, на което да преработя това. Там нищо не те разсейва, там всичко е природно, перфектно, няма какво да му мислиш. Планинарството е по-пасивно, ти присъстваш. Впечатли ме Грузия. Там е страхотно зелено на същата надморска височина, на която в България вече няма толкова растителност, защото липсва вода. В същото време си обграден от четири-петхилядници. Хората са успели да запазят живота си на село – те са запознати със света, все пак живеят на място, през което ежедневно минават по десетина туристи. Но са съхранили усещането си за нормалност.
Хората, които тихо и кротко променят средата, формират общности и задават посоки, в които има смисъл да тръгнем заедно. Тук ви срещаме с тях. Това са „Тези хора“.
Shortly after the first set of explosions, Iranians received bursts of notifications on their phones. They came not from the government advising caution, but from an apparently hacked prayer-timing app called BadeSaba Calendar that has been downloaded more than 5 million times from the Google Play Store.
The messages arrived in quick succession over a period of 30 minutes, starting with the phrase ‘Help has arrived’ at 9:52 am Tehran time, shortly after the first set of explosions. No party has claimed responsibility for the hacks.
It happened so fast that this is most likely a government operation. I can easily envision both the US and Israel having hacked the app previously, and then deciding that this is a good use of that access.
When you need to use a proxy to keep your zero trust environment secure, it often comes with a cost: poor performance for your users. Soon after deploying a client proxy, security teams are generally slammed with support tickets from users frustrated with sluggish browser speed, slow file transfers, and video calls glitching at just the wrong moment. After a while, you start to chalk it up to the proxy — potentially blinding yourself to other issues affecting performance.
We knew it didn’t have to be this way. We knew users could go faster, without sacrificing security, if we completely re-built our approach to proxy mode. So we did.
In the early days of developing the device client for our SASE platform, Cloudflare One, we prioritized universal compatibility. When an admin enabled proxy mode, the Client acted as a local SOCKS5 or HTTP proxy. However, because our underlying tunnel architecture was built on WireGuard, a Layer 3 (L3) protocol, we faced a technical hurdle: how to get application-layer (L4) TCP traffic into an L3 tunnel. Moving from L4 to L3 was especially difficult because our desktop Client works across multiple platforms (Windows, macOS, Linux) so we couldn’t use the kernel to achieve this.
To get over this hurdle, we used smoltcp, a Rust-based user-space TCP implementation. When a packet hit the local proxy, the Client had to perform a conversion, using smoltcp to convert the L4 stream into L3 packets for the WireGuard tunnel.
While this worked, it wasn’t efficient. Smoltcp is optimized for embedded systems, and does not support modern TCP features. In addition, in the Cloudflare edge, we had to convert the L3 packets back into an L4 stream. For users, this manifested as a performance ceiling. On media-heavy sites where a browser might open dozens of concurrent connections for images and video, and the lack of a high performing TCP stack led to high latency and sluggish load times when even on high-speed fiber connections, proxy mode felt significantly slower than all the other device client modes.
Introducing direct L4 proxying with QUIC
To solve this, we’ve re-built the Cloudflare One Client’s proxy mode from the ground up and deprecated the use of WireGuard for proxy mode, so we can capitalize on the capabilities of QUIC. We were already leveraging MASQUE (part of QUIC) for proxying IP packets, and added the usage of QUIC streams for direct L4 proxying.
By leveraging HTTP/3 (RFC 9114) with the CONNECT method, we can now keep traffic at Layer 4, where it belongs. When your browser sends a SOCKS5 or HTTP request to the Client, it is no longer broken down into L3 packets.
Instead, it is encapsulated directly into a QUIC stream.
This architectural shift provides three immediate technical advantages:
Bypassing smoltcp: By removing the L3 translation layer, we eliminate IP packet handling and the limitations of smoltcp’s TCP implementation.
Native QUIC Benefits: We benefit from modern congestion control and flow control, which are handled natively by the transport layer.
Tuneability: The Client and Cloudflare’s edge can tune QUIC’s parameters to optimize performance.
In our internal testing, the results were clear: download and upload speeds doubled, and latency decreased significantly.
Who benefits the most
While faster is always better, this update specifically unblocks three key common use cases.
First, in coexistence with third-party VPNs where a legacy VPN is still required for specific on-prem resources or where having a dual SASE setup is required for redundancy/compliance, the local proxy mode is the go-to solution for adding zero trust security to web traffic. This update ensures that “layering” security doesn’t mean sacrificing the user experience.
Second, for high-bandwidth application partitioning, proxy mode is often used to steer specific browser traffic through Cloudflare Gateway while leaving the rest of the OS on the local network. Users can now stream high-definition content or handle large datasets without sacrificing performance.
Finally, developers and power users who rely on the SOCKS5 secondary listener for CLI tools or scripts will see immediate improvements. Remote API calls and data transfers through the proxy now benefit from the same low-latency connection as the rest of the Cloudflare global network.
How to get started
The proxy mode improvements are available with minimum client version 2025.8.779.0 for Windows, macOS, and Linux devices. To take advantage of these performance gains, ensure you are running the latest version of the Cloudflare One Client.
Log in to the Cloudflare One dashboard.
Navigate to Teams & Resources > Devices > Device profiles > General profiles.
Select a profile to edit or create a new one and ensure the Service mode is set to Local proxy mode and the Device tunnel protocol is set to MASQUE.
You can verify your active protocol on a client machine by running the following command in your terminal:
warp-cli settings | grep protocol
Visit our documentation for detailed guidance on enabling proxy mode for your devices.
The public Internet relies on a fundamental principle of predictable routing: a single IP address points to a logically unique destination. Even in an Anycast architecture like Cloudflare’s, where one IP is announced from hundreds of locations, every instance of that IP represents the same service. The routing table always knows exactly where a packet is intended to go.
This principle holds up because global addressing authorities assign IP space to organizations to prevent duplication or conflict. When everyone adheres to a single, authoritative registry, a routing table functions as a source of absolute truth.
On the public Internet, an IP address is like a unique, globally registered national identity card. In private networks, an IP is just a name like “John Smith”, which is perfectly fine until you have three of them in the same room trying to talk to the same person.
As we expand Cloudflare One to become the connectivity cloud for enterprise backbones, we’ve entered the messy reality of private IP address space. There are good reasons why duplication arises, and enterprises need solutions to handle these conflicts.
Today, we are introducing Automatic Return Routing (ARR) in Closed Beta. ARR is an optional tool for Cloudflare One customers that gives you the flexibility to route traffic back to where it originated, without requiring an IP route in a routing table. This capability allows overlapping networks to coexist without a single line of Network Address Translation (NAT) or complex Virtual Routing and Forwarding (VRF) configuration.
The ambiguity problem
In enterprise networking, IP overlap is a fact of life. We see it in three common scenarios that traditionally cause toil for admins:
Mergers & acquisitions: Two companies merge, and both use 10.0.1.0/24 for their core services.
Extranets: Partners, vendors or customers securely connect to your network using their own internal IP schemes, leading to unavoidable conflicts.
Cookie-cutter architectures: SaaS providers or retail brands use identical IP space for every branch to simplify deployment and operation.
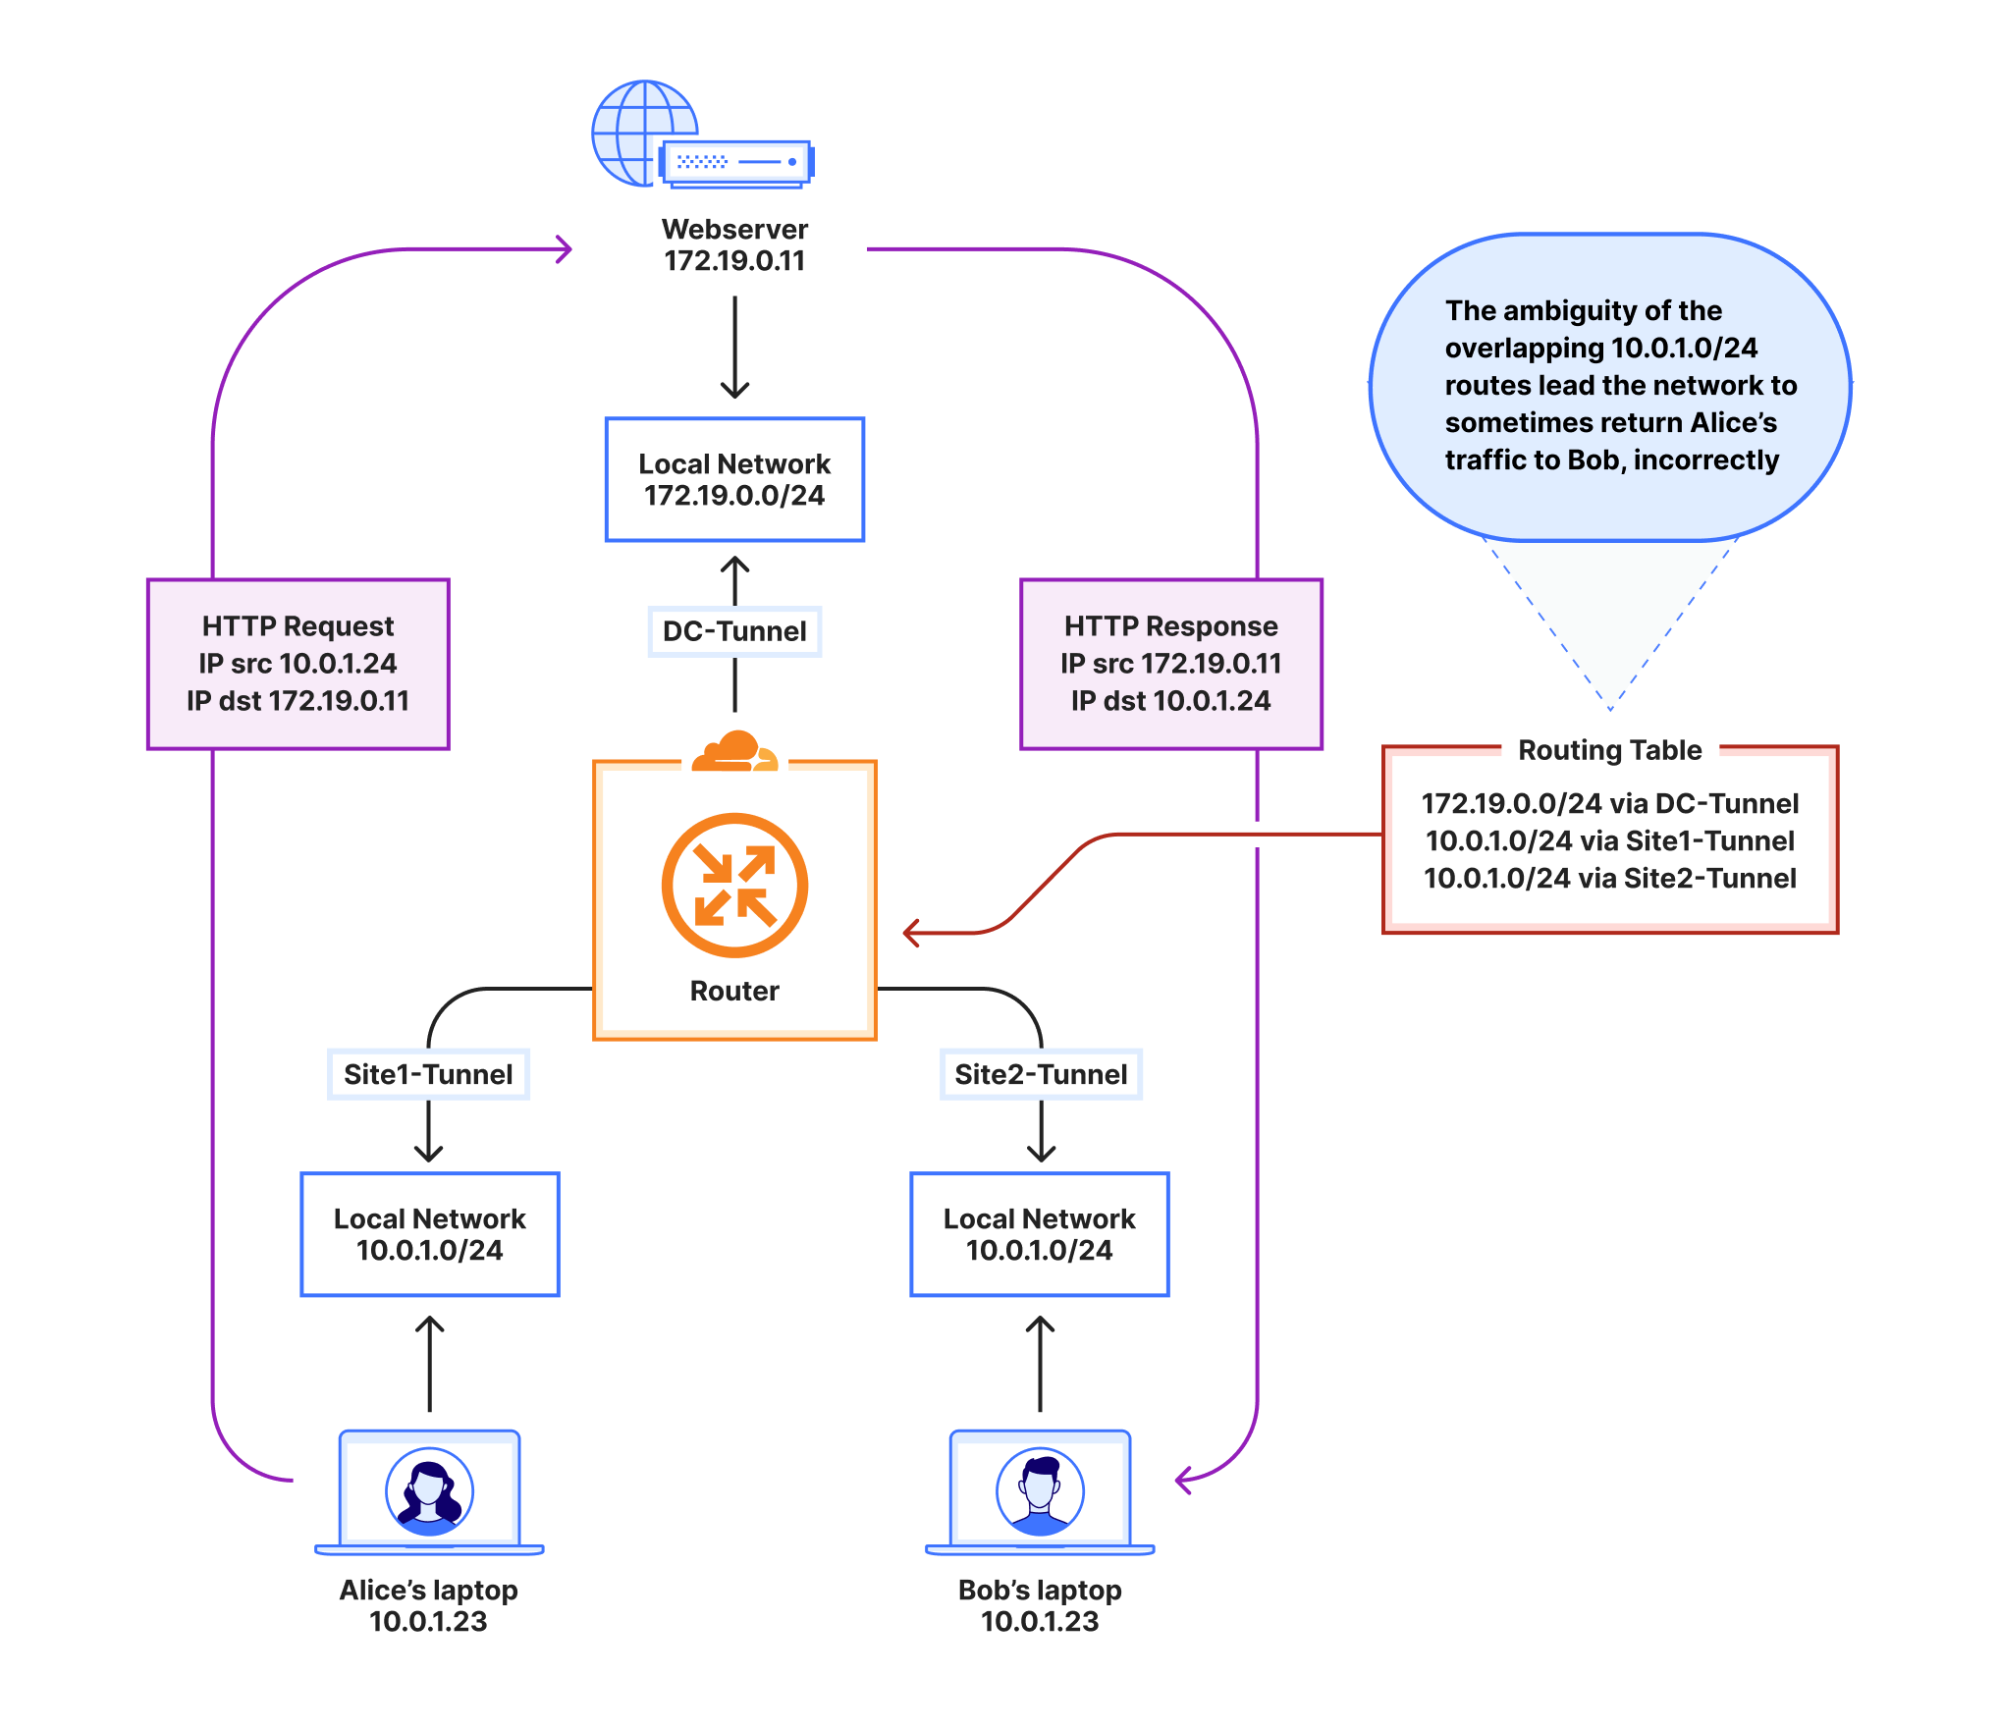
The problem arises when these sites try to talk to the Internet or a data center through Cloudflare. If two different sites send traffic from the same source IP, the return packet hits an architectural wall. The administrator has to make a decision on how to route the traffic based on the ambiguous destination. If the administrator puts both routes into the routing table, it will be non-deterministic as to which path is taken: the correct path or the incorrect path. From the perspective of a standard routing table, there is no way to distinguish between two identical paths.
This diagram shows two branches (Site A and Site B) both using 10.0.1.0/24. They send packets to Cloudflare. The return packet from the Internet reaches the Cloudflare edge, and this return traffic is sometimes sent to the wrong site because the routing table has two identical egress options.
Why traditional fixes fail
There are numerous ways to resolve this ambiguity, and we are committed to solving them in the easiest way for our customers to manage. The traditional “industry standard” fixes are functional, but they introduce significant administrative overhead and complexity that we are committed to eliminating:
Virtual Routing and Forwarding (VRF): This involves creating “virtual” routing tables to keep traffic isolated. While effective for separation, it adds administrative overhead. Managing cross-VRF communication (route leaking) is brittle and complex at scale.
Network Address Translation (NAT): You can NAT each overlapping subnet from an unmanaged IP space to a managed IP range that is unique in your network. This approach works well, but the mapping is administrative toil for each new site or partner.
Typically, the use case we hear from customers is an overlapping network needing to access the Internet or a private data center. How do we solve this without administrative overhead?
Introducing Automatic Return Routing (ARR)
We developed ARR as a “zero-touch” solution to this problem. ARR moves the intelligence from the routing table to stateful tracking.
So what is stateful tracking?
In traditional networking, a router is “forgetful” (aka “stateless”). It treats every single packet like a total stranger. Even if it just saw a packet from the exact same source going to the exact same destination a millisecond ago, it has to look at its routing table all over again to decide where to send the next one.
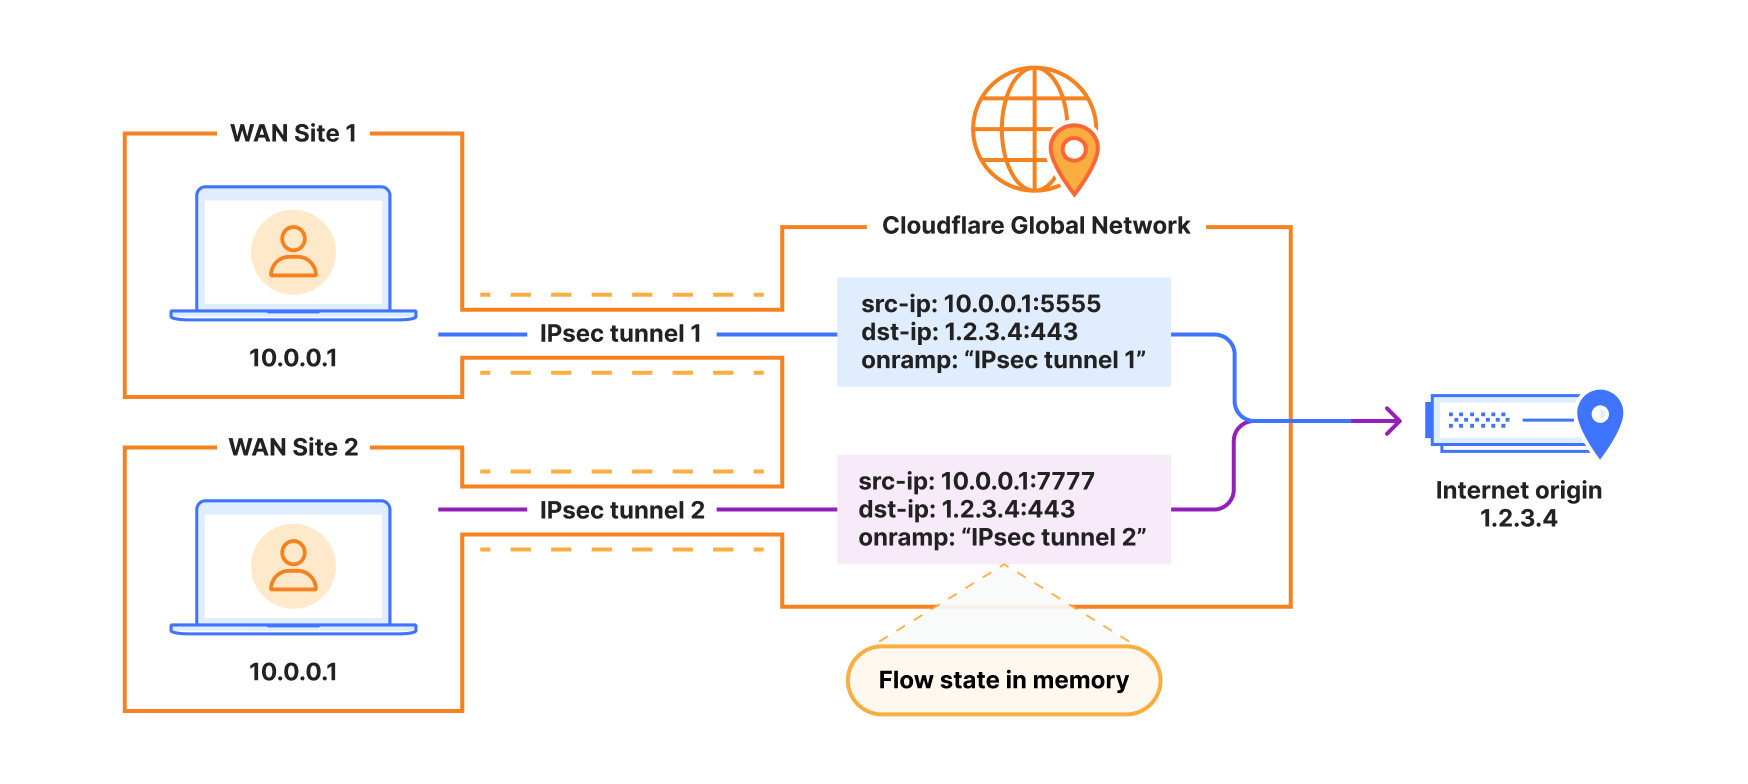
With stateful tracking, the system has a memory. It recognizes when a series of packets are all part of the same “flow” (that is, a network conversation between two endpoints), and remembers key information about that flow until it finishes. With ARR, we remember one extra piece of information when initializing the flow: the specific tunnel that initiated it. This allows us to send return traffic back to that same tunnel, without ever consulting a routing table!
Instead of asking the network, “Where does this IP live?” ARR asks, “Where did this specific conversation originate?”
Flow Matching: The Cloudflare Virtual Network first checks (by header inspection) whether that packet matches an existing flow.
Proxying: If the packet matches, that’s great! All of the decisions about this traffic have already been made and stored in our memory. All we need to do is pass that packet along already-established paths.
Flow Setup: If it doesn’t match an existing flow, we decide which parts of the Cloudflare One stack to pass it through (e.g. Gateway, DLP, Firewall), as well as its ultimate destination. We store all of this state in memory. With ARR, this is when we record which tunnel initiated the flow.
Symmetric Return: When return traffic arrives from the destination, the Cloudflare Virtual Network uses its existing in-memory state to proxy the traffic. Crucially, it does this without needing to examine the traffic’s destination IP, which could very well be reused across different sites. This completely bypasses the need to consult a routing table. We see the originating tunnel in the flow state and deliver the packet directly back to it.
Example of overlapping source IPs tracked by in-memory flow state, tagged with source onramp to inform return routing decision.
By remembering the originating tunnel for every flow, ARR facilitates zero-touch routing. If your site traffic is only client-to-Internet, there is no need to configure return routes at all, reducing toil when deploying new branch sites or “Coffee Shop Networking.”
Built on Unified Routing
To make ARR a reality at Cloudflare scale, we plugged into another initiative we have been working on: Unified Routing.
Historically, Cloudflare Zero Trust (users/proxies) and Cloudflare WAN (network-layer/sites) lived at different levels of the system. Cloudflare WAN relied on kernel primitives (Linux network namespaces, routes, eBPF, etc). Zero Trust lived in userspace, where proxies could perform deep inspection and application-level security. This “split-brain” approach often required complex logic to move traffic between component services, and some of this complexity became product limitations that customers might notice.
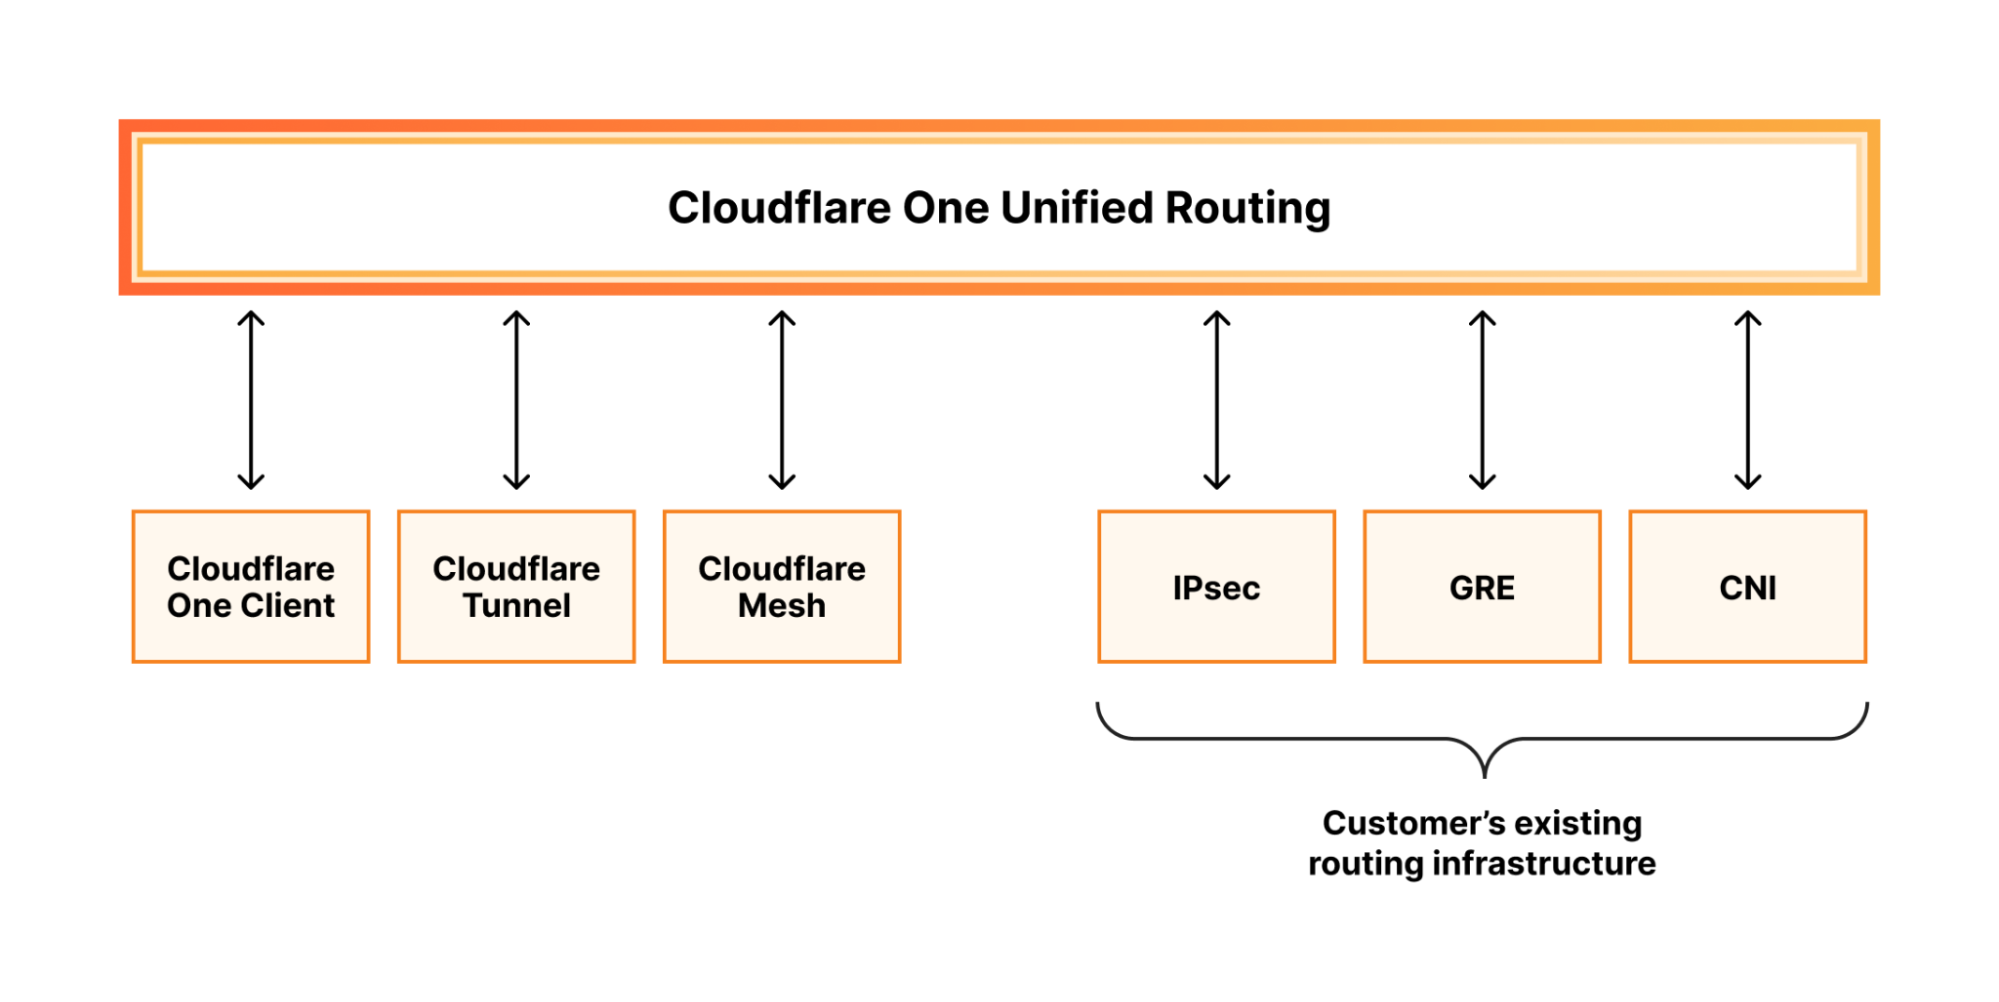
With our new Unified Routing mode, we have moved the initial routing decision from our network-layer data plane into our existing Zero Trust userspace routing logic, the same hardened software used by Cloudflare One Clients and Cloudflare Tunnel in our Zero Trust solution. This change has many benefits to how we enable our customers to use their private networks with products across the Cloudflare platform, as it fixes long-standing interoperability problems between Cloudflare WAN and Zero Trust. Unified Routing means you can use Cloudflare Mesh, Cloudflare Tunnel, and IPsec/GRE on-ramps together in the same account without a single conflict.
In September 2025, we deployed Unified Routing mode internally for all Cloudflare employees and sites. We saw immediate 3-5x performance improvements for Cloudflare One Clients, as you can see in the graph above.
When designing ARR, we knew that we needed to move away from kernel-based routing and build on our new Unified Routing framework.
When Unified Routing is enabled, all Cloudflare WAN traffic flows through Apollo, our Zero Trust hub. Unlike the Linux kernel’s standard routing table, our userspace data plane is fully programmable. We can attach metadata, like the originating Tunnel ID, directly to a flow entry in Apollo.
Each packet is tracked by flow from the moment it hits our edge, and we no longer need to make independent, per-packet routing decisions. Instead, we can make consistent, session-aware decisions for the lifetime of the flow.
Once enabled for a tunnel or interconnect, any traffic that matches an existing flow is routed back to the connection where it originated, without consulting the routing table.
Putting ARR to work
For the enterprise architect, ARR is a tool to bypass the persistent friction of IP address conflicts. Whether integrating an acquisition or onboarding a partner, the goal is to make the network invisible, so you can focus on the applications, not the plumbing.
Today, ARR is in closed beta and supports overlapping IP addresses accessing the Internet via our Secure Web Gateway. We are already extending this to support private data center access, adding mid-flow failover (pinning the flow to a primary onramp, and seamlessly detecting when that flow fails over to a backup onramp), and further investing in the architectural capabilities needed to make IP overlap a non-issue for even the most complex global deployments.
Not using Cloudflare One yet? Start now with our Free and Pay-as-you-go plans to protect and connect your users and networks, and contact us for comprehensive private WAN connectivity via IPsec and private interconnect.
Amazon Web Services (AWS) successfully completed the annual recertification audit with no findings for ISO 9001:2015, 27001:2022, 27017:2015, 27018:2019, 27701:2019, 20000-1:2018, 22301:2019, and Cloud Security Alliance (CSA) STAR Cloud Controls Matrix (CCM) v4.0. The objective of the audit was to enable AWS to expand their ISO and CSA STAR certifications to include one new AWS Region and one new AWS service to the scope. The ISO standards cover areas including quality management, information security, cloud security, privacy protection, service management, and business continuity. The certifications demonstrate the commitment of AWS to maintaining robust security controls and protecting customer data across our services.
As part of this recertification audit, one new Region [Asia Pacific (Taipei)] and one new service (AWS Deadline Cloud) were added into the scope since the last certification issued November 25, 2025.
For a full list of AWS services that are certified under ISO and CSA Star, see the AWS ISO and CSA STAR Certified page. Customers can also access the certifications in the AWS Management Console through AWS Artifact.
If you have feedback about this post, submit comments in the Comments section below.
Do you find yourself constantly looking up the difference between container_memory_usage_bytes, container_memory_working_set_bytes, and container_memory_rss? Pick the wrong one and your memory limits lie to you, your benchmarks mislead you, and your container gets OOMKilled.
The explanation is simple: RAM is not used in just one way. One of the easiest things to miss is the page cache semantics. For some containers, memory taken by page caching can make up most of the reported usage, even though that memory is largely reclaimable, creating surprising differences between those metrics.
NOTE: The feature discussed here currently only supports Linux.
Prometheus writes a lot of data to disk. It is, after all, a database. But not every write benefits from sitting in the page cache. Compaction writes are the clearest example: once a block is written, only a fraction of that data is likely to be queried again soon, and since there is no way to predict which fraction, caching it all offers little return. The use-uncached-io feature flag was built to address exactly this.
Bypassing the cache for those writes reduces Prometheus’s page cache footprint, making its memory usage more predictable and easier to reason about. It also relieves pressure on that shared cache, lowering the risk of evicting hot data that queries and other reads actually depend on. A potential bonus is reduced CPU overhead from cache allocations and evictions. The hard constraint throughout was to avoid any measurable regression in CPU or disk I/O.
The flag was introduced in Prometheus v3.5.0 and currently only supports Linux. Under the hood, it uses direct I/O, which requires proper filesystem support and a kernel v2.4.10 or newer, though you should be fine, as that version shipped nearly 25 years ago.
If direct I/O helps here, why was it not done earlier, and why is it not used everywhere it would help? Because direct I/O comes with strict alignment requirements. Unlike buffered I/O, you cannot simply write any chunk of memory to any position in a file. The file offset, the memory buffer address, and the transfer size must all be aligned to the logical sector size of the underlying storage device, typically 512 or 4096 bytes.
To satisfy those constraints, a bufio.Writer-like writer, directIOWriter, was implemented. On Linux kernels v6.1 or newer, Prometheus retrieves the exact alignment values via statx; on older kernels, conservative defaults are used.
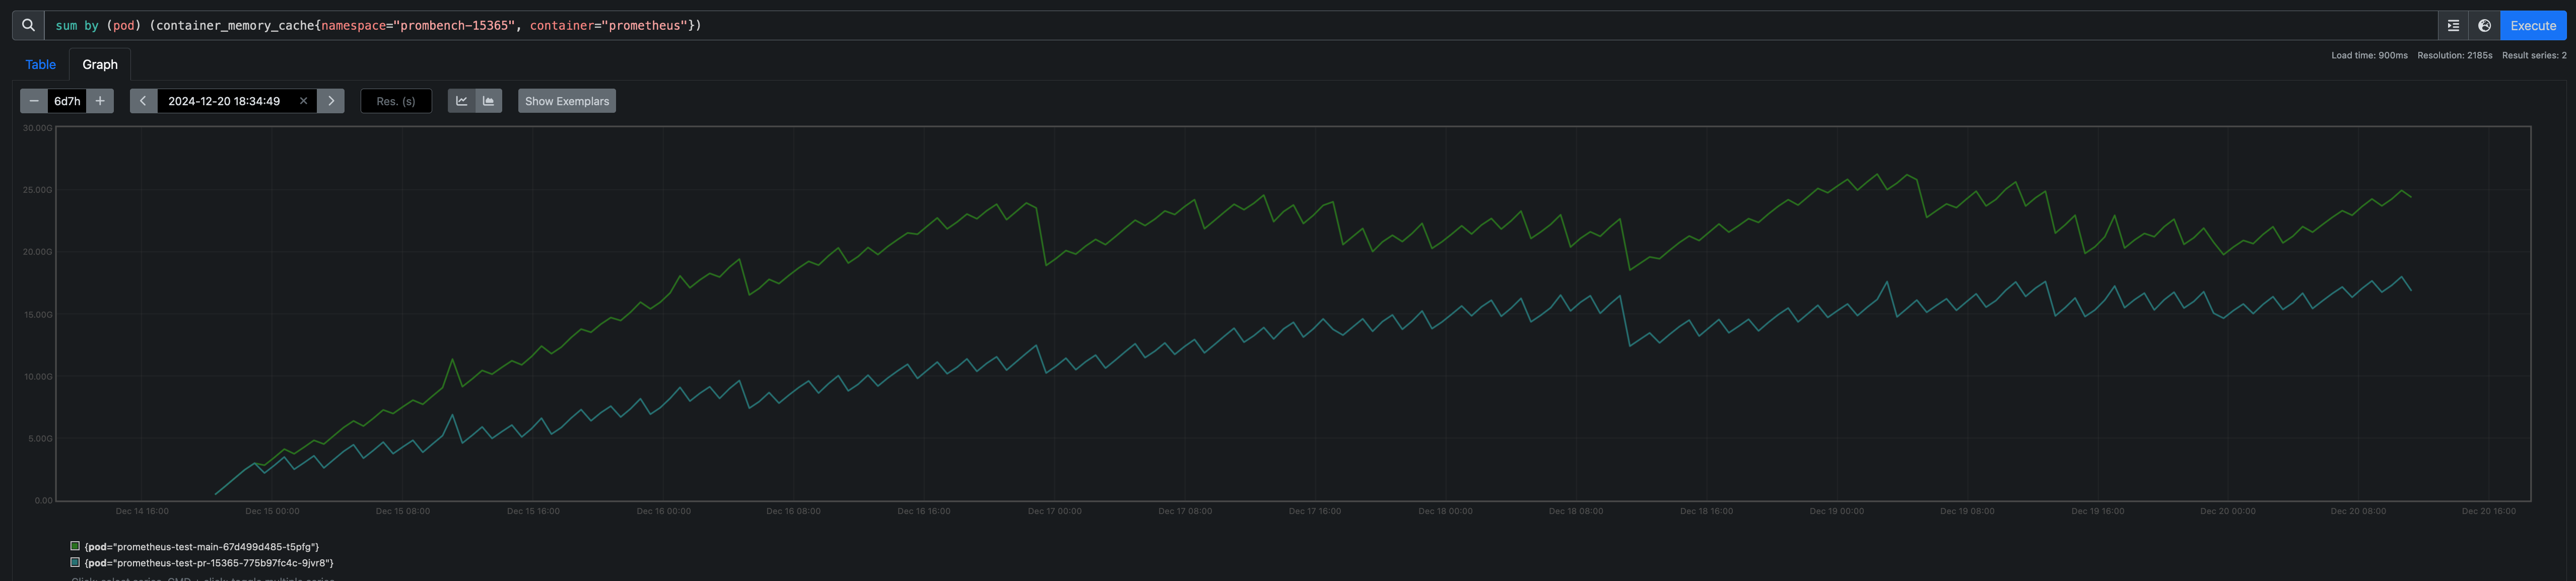
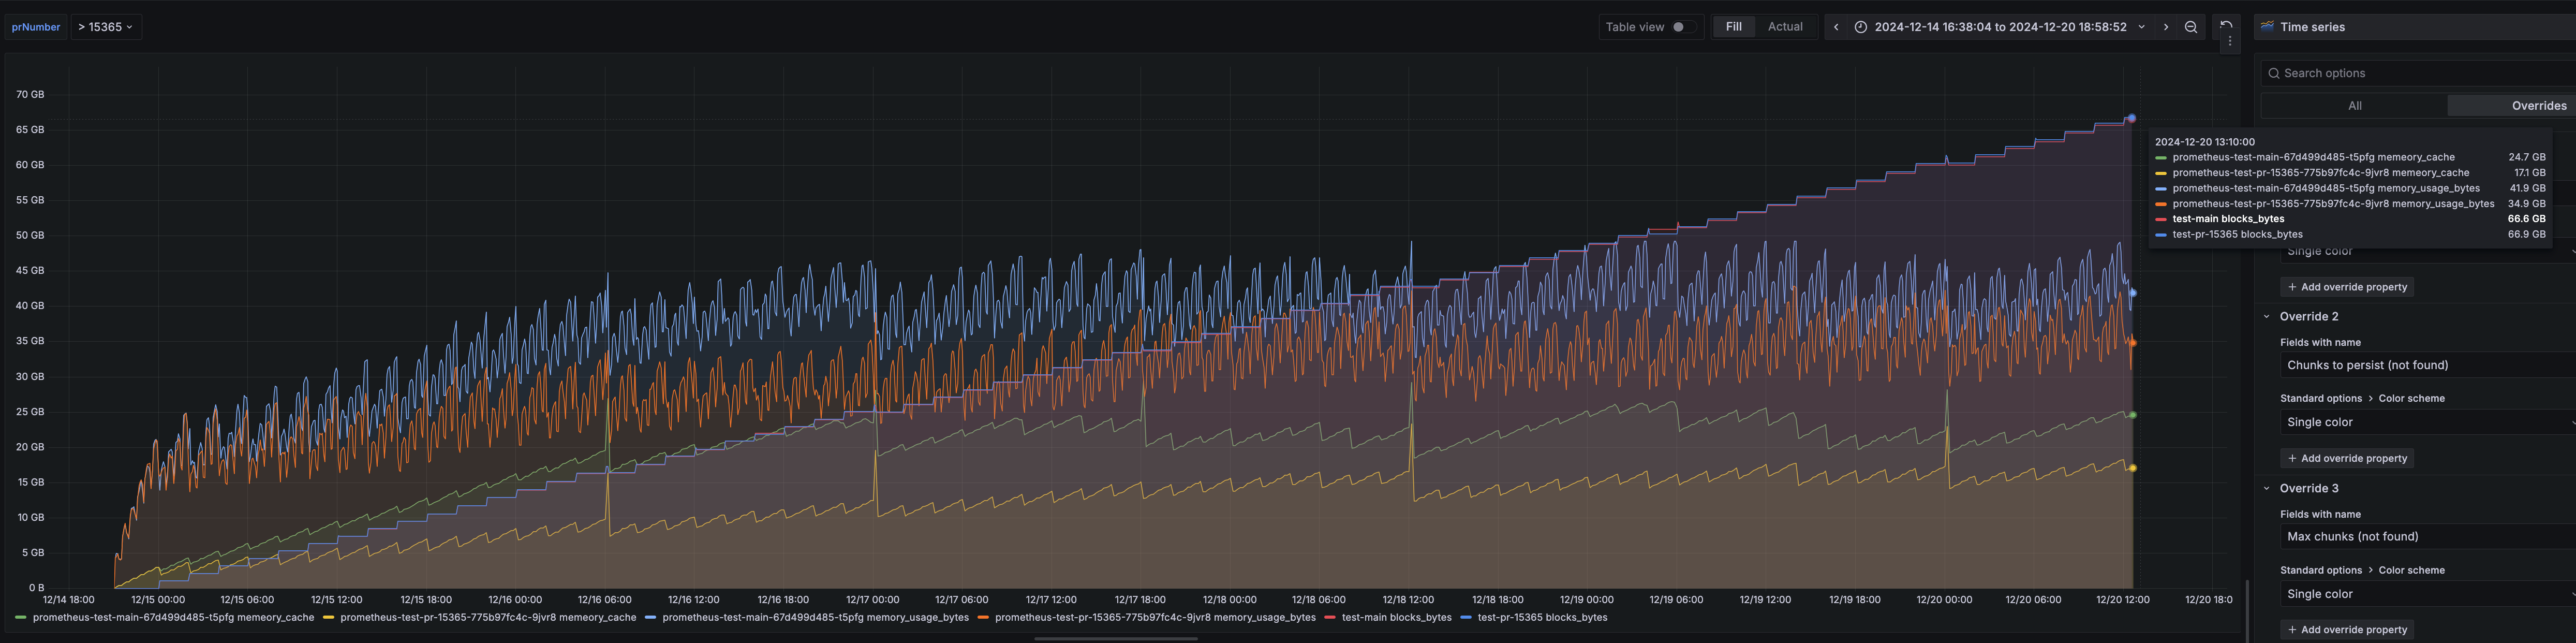
The directIOWriter currently covers chunk writes during compaction only, but that alone accounts for a substantial portion of Prometheus’s I/O. The results are tangible: benchmarks show a 20–50% reduction in page cache usage, as measured by container_memory_cache.
The work is not done yet, and contributions are welcome. Here are a few areas that could help move the feature closer to General Availability:
Covering more write paths
Direct I/O is currently limited to chunk writes during compaction. Index files and WAL writes are natural next candidates, although they would require some additional work.
Building more confidence around directIOWriter
All existing TSDB tests can be run against the directIOWriter using a dedicated build tag: go test --tags=forcedirectio ./tsdb/. More tests covering edge cases for the writer itself would be welcome, and there is even an idea of formally verifying that it never violates alignment requirements.
Experimenting with RWF_DONTCACHE
Introduced in Linux kernel v6.14, RWF_DONTCACHE enables uncached buffered I/O, where data still goes through the page cache but the corresponding pages are dropped afterwards. It would be worth benchmarking whether this delivers similar benefits without direct I/O’s alignment constraints.
Support beyond Linux
Support is currently Linux-only. Contributions to extend it to other operating systems are welcome.
For more details, see the proposal and the PR that introduced the feature.
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.