Post Syndicated from Explosm.net original https://explosm.net/comics/rich
New Cyanide and Happiness Comic
Post Syndicated from Explosm.net original https://explosm.net/comics/rich
New Cyanide and Happiness Comic
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2025/06/friday-squid-blogging-squid-run-in-southern-new-england.html
Southern New England is having the best squid run in years.
As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.
Post Syndicated from Chinmaee Parulekar original https://aws.amazon.com/blogs/security/2025-iso-and-csa-star-certificates-now-available-with-three-new-regions/
Amazon Web Services (AWS) successfully completed an onboarding audit with no findings for ISO 9001:2015, 27001:2022, 27017:2015, 27018:2019, 27701:2019, 20000-1:2018, and 22301:2019, and Cloud Security Alliance (CSA) STAR Cloud Controls Matrix (CCM) v4.0. EY CertifyPoint auditors conducted the audit and reissued the certificates on May 26, 2025. The objective of the audit was to assess the level of compliance with the requirements of the applicable international standards.
During this onboarding audit, we onboarded three new AWS Regions [Asia Pacific (Thailand), Asia Pacific (Malaysia), Mexico (Central)] to the scope since the last certification issued on February 19, 2025.
For a full list of AWS services that are certified under ISO and CSA Star, see the AWS ISO and CSA STAR Certified page. Customers can also access the certifications in the AWS Management Console through AWS Artifact.
If you have feedback about this post, submit comments in the Comments section below.
Post Syndicated from LastWeekTonight original https://www.youtube.com/watch?v=fUroqGyWz90
Post Syndicated from Jeremy Stieglitz original https://aws.amazon.com/blogs/security/how-to-use-on-demand-rotation-for-aws-kms-imported-keys/
Today, we’re announcing support for on-demand rotation of symmetric encryption AWS Key Management Service (AWS KMS) keys with imported key material (EXTERNAL origin). This new capability enables you to rotate the cryptographic key material of these keys without changing the key identifier (key ID or Amazon Resource Name (ARN)). Rotating keys helps you meet compliance requirements and security best practices that mandate periodic key rotation.
AWS KMS has long supported automatic key rotation for AWS KMS keys whose key material is generated by AWS KMS (AWS_KMS origin). Until now, AWS KMS customers who imported their own key material could not rotate that material without creating a new KMS key. This process called manual rotation required updating references to the older key identifiers. With today’s launch, the key ID of the imported key remains unchanged after rotation, so existing workloads are not disrupted. In this post, we tell you how the new capability works, look at key material expiry and deletion features unique to imported keys, and review pricing for this new feature.
When you create an AWS KMS key with EXTERNAL origin, AWS KMS assigns a fixed identifier to the key called the key ID. However, AWS KMS doesn’t generate key material for the cryptographic operations. You must import your own key material using the ImportKeyMaterial operation.
When you import key material, AWS KMS computes a unique key material identifier based on the key ID and the key material. Even if you import the same key material in different keys, AWS KMS will assign distinct key material identifiers. This computation uses a cryptographic hash so the key material identifier doesn’t reveal information about the key material itself. AWS KMS embeds this key material identifier in the ciphertext blob produced by symmetric encryption.
Until now, after you imported key material into an AWS KMS key, you could not import additional key material into that key to rotate the key. With this new feature launch, you can associate multiple imported key materials with a single, symmetric-encryption key. You can use the RotateKeyOnDemand operation to make the most recently imported key material the current key material. AWS KMS uses the current key material to generate new ciphertext. Unless deleted or expired, the other key materials remain available for decryption. When you present ciphertext for decryption, AWS KMS automatically selects the correct key material using the key material identifier embedded in the ciphertext.
To help improve the auditability that keys have rotated, we’ve added new identifiers in KMS API responses for the specific key material used. The KeyMaterialId is a new field that AWS KMS will return in addition to the KeyId. Similarly, the DescribeKey response for these keys now displays the identifier of the current key material as CurrentKeyMaterialId. The inclusion of the KeyMaterialId and CurrentKeyMaterialId in API responses makes key rotation more transparent.
Before we dive into the details, the following is an outline of the overall process to rotate an imported key:
EXTERNAL originCurrentKeyMaterialId displayed in the DescribeKey response.ImportType input parameter which lets you inform AWS KMS whether you are associating new key material with a key (--import-type NEW_KEY_MATERIAL) or re-importing previously associated key material (--import-type EXISTING_KEY_MATERIAL).--include-key-material ALL_KEY_MATERIAL to view both key materials. The key material state of the second key material will be PENDING_ROTATION.OnDemandRotationStartDate only while the rotation is in progress.ListKeyRotations with --include-key-material ALL_KEY_MATERIAL after rotation completes to view key materials associated with this key. The KeyMaterialState of the new key material you imported will change from PENDING_ROTATION to CURRENT. The key material state of the first key material will change from CURRENT to NON_CURRENT.CurrentKeyMaterialId is used for creating ciphertext, but the key material used for decryption is automatically determined by AWS KMS.The following is a sample sequence of AWS KMS commands to exercise the import key rotation functionality using the AWS Command Line Interface (AWS CLI). The specific commands that follow work in Linux or MacOS environments and might need to be modified for use in a Windows environment. This functionality can also be exercised through the AWS SDKs. These operations, except for wrapping a key material for import, generate-data-key, and decrypt can be initiated in the AWS Management Console.
This section should be familiar to anyone who has used the existing import key functionality in AWS KMS.
EXTERNAL origin and save the key ARN. The initial state of this key is PendingImport.
get-parameters-for-import command to create the wrapping key and import token and save them to files. AWS KMS supports multiple wrapping algorithms; we use RSAES_OAEP_SHA_256 with a 4096-bit RSA key in the following example. The value of the ImportToken and PublicKey fields in the response has been trimmed for brevity.
ListKeyRotations API response. We also capture the key material ID from the response. In this example, the key material doesn’t expire. Optionally, you can set an expiration time.
CurrentKeyMaterialId in the DescribeKey response should match ${KEY_MATERIAL1_ID}
ListKeyRotations to view key materials associated with the key. There should only be one key material with the same ID as in ${KEY_MATERIAL1_ID} and with a key material state of CURRENT.
This step demonstrates how to verify the key material ID of your imported key in cryptographic operations.
GenerateDataKey operation and capture the ciphertext. This operation returns a data key in both plaintext and ciphertext form. The KeyMaterialId in the response matches the identifier for the first key material.
KeyMaterialId in the response matches the identifier for the first key material. The plaintext in decrypt response matches the plaintext data key in the GenerateDataKey response.
Import key rotations start with importing new key material into this key.
get-parameters-for-import command to create the wrapping key and import token for the second key material to be imported. The value of the ImportToken and PublicKey fields in the response has been trimmed for brevity.
Note: This call will fail if you omit the
import-type parameteror set it toEXISTING_KEY_MATERIAL. Specifyingimport-typeasNEW_KEY_MATERIALallows the API caller to associate additional key material with the imported key.
ListKeyRotations to view key materials associated with the key. There should now be two key materials. The key material state of the second key material should be PENDING_ROTATION.
CurrentKeyMaterialId in DescribeKey response should still be ${KEY_MATERIAL1_ID}.
This step moves the current key material for this key to the newly imported key material.
RotateKeyOnDemand operation to initiate an on-demand key rotation. If the key material in PENDING_ROTATION state is deleted or expires before initiating on-demand rotation, this operation will fail.
GetKeyRotationStatus command to monitor the rotation status. Until the rotation is completed, the GetKeyRotationStatus response will include the OnDemandRotationStartDate field. When this field disappears, the on-demand key rotation is complete.
ListKeyRotations when rotation completes. The second key material changes state from PENDING_ROTATION to CURRENT.
CurrentKeymaterialId field in the DescribeKey response. It should now match ${KEY_MATERIAL2_ID}.
Similar to Step 2, this step demonstrates how to verify that the key material ID of your imported key in cryptographic operations has been rotated.
GenerateDataKey operation and capture the ciphertext. This operation returns a data key in both plaintext and ciphertext forms. Note that the KeyMaterialId returned in the response matches the identifier of the second key material.
KeyMaterialId returned in the response matches the identifier of the second key material. The plaintext in decrypt response matches the plaintext data key in the previous GenerateDataKey response.
With the launch of this feature, the DeleteImportedKeyMaterial operation takes an optional KeyMaterialId parameter. If no KeyMaterialId is specified, AWS KMS deletes the current key material. This maintains backwards compatibility with existing behavior.
PendingImport.
ListKeyRotations also reflects the first key material as PendingImport.
KMSInvalidStateException when a key is in PendingImport state even though the key material required to decrypt the specific ciphertext blob is imported into AWS KMS.
You need to re-import all expired or deleted key materials associated with a key for the key to become usable again.
DescribeKey to validate the key is now enabled.
AWS CloudTrail now includes the key material ID in the additionalEventData field for operations using symmetric-encryption keys (both AWS_KMS and EXTERNAL origin). The following is a sample CloudTrail event for the AWS KMS decrypt operation:
Unlike standard KMS keys that you create within AWS KMS, imported keys offer two unique capabilities for enhanced controls over key material within AWS.
Key expiry and import key material deletion can be useful if you need to demonstrate immediate key suspension in the cloud or when you want to temporarily seed AWS KMS with key material that can be inserted and repeatedly removed from cloud access (hydration and re-hydration of keys for improved digital sovereignty).
AWS KMS is designed to keep imported key material highly available. But AWS KMS doesn’t maintain the durability of imported key material at the same level as key material that AWS KMS generates. You must retain a copy of the imported key material outside of AWS KMS in a system that you control. We recommend that you store an exportable copy of the imported key material in a key management system, such as an HSM. As a best practice, you should store a reference to the KMS key ARN and key material description alongside the exportable copy of the key material.
The deletion or expiration of any key material associated with a KMS key makes that key unusable. You must re-import all the key materials associated with a key before it can be used for cryptographic operations.
The following types of KMS keys with imported key material do not support on-demand key rotation, but you can continue to use manual rotation with these keys.
This new capability includes several important features:
For AWS KMS keys that rotate automatically or on-demand, each key incurs a base cost, and the first two rotations add $1 per month (prorated hourly) in additional charges. The pricing is capped after the second rotation, meaning subsequent rotations beyond the second one aren’t billed. This simplified pricing provides you with more predictable costs while maintaining the flexibility to rotate keys frequently to meet your compliance and security audit requirements.
You can start using this feature today in all AWS Regions where AWS KMS is available. To learn more, visit the AWS KMS Developer Guide.
We’re excited to see how you use this new capability to enhance your key management practices. Leave a comment below or on the AWS re:Post community forum to let us know what you think.
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2025/06/hearing-on-the-federal-government-and-ai.html
On Thursday I testified before the House Committee on Oversight and Government Reform at a hearing titled “The Federal Government in the Age of Artificial Intelligence.”
The other speakers mostly talked about how cool AI was—and sometimes about how cool their own company was—but I was asked by the Democrats to specifically talk about DOGE and the risks of exfiltrating our data from government agencies and feeding it into AIs.
Post Syndicated from Narayani Ambashta original https://aws.amazon.com/blogs/big-data/simplify-real-time-analytics-with-zero-etl-from-amazon-dynamodb-to-amazon-sagemaker-lakehouse/
At AWS re:Invent 2024, we introduced a no code zero-ETL integration between Amazon DynamoDB and Amazon SageMaker Lakehouse, simplifying how organizations handle data analytics and AI workflows. This integration alleviates the traditional challenges of building and maintaining complex extract, transform, and load (ETL) pipelines for transforming NoSQL data into analytics-ready formats, which previously required significant time and resources while introducing potential system vulnerabilities. Organizations can now seamlessly combine the strength of DynamoDB in handling rapid, concurrent transactions with immediate analytical processing through the zero-ETL integration. For example, an ecommerce platform storing user session data and cart information in DynamoDB can now analyze this data in near real time without building custom pipelines. Gaming companies using DynamoDB for player data can instantly analyze user behavior as events occur, enabling real-time insights into game balance and player engagement patterns.
The zero-ETL capability uses built-in change data capture (CDC) to automatically synchronize data updates and schema changes between DynamoDB and SageMaker Lakehouse tables. By using Apache Iceberg format, the integration provides reliable performance with ACID transaction support and efficient large-scale data handling. Data scientists can train ML models on fresh data and data analysts can generate reports using current information, with typical synchronization latency in minutes rather than hours.
In this post, we share how to set up this zero-ETL integration from DynamoDB to your SageMaker Lakehouse environment.
We use a SageMaker Lakehouse catalog, AWS Lake Formation, Amazon Athena, AWS Glue, and Amazon SageMaker Unified Studio for this integration. The following is the reference data flow diagram for the zero-ETL integration.

The workflow consists of the following components:
In this section, we walk through the steps to set up your solution resources and confirm your permission settings.
Before you begin, you need an AWS Identity and Access Management (IAM) role for enabling the zero-ETL integration. In this post, we use SageMaker Unified Studio, which offers a unified data platform experience. It automatically manages required Lake Formation permissions on data and catalogs for you.
You have to first create a SageMaker Unified Studio domain, an administrative entity that controls user access, permissions, and resources for teams working within the SageMaker Unified Studio environment. Note down the SageMaker Unified Studio URL after you create the domain. You will be using this URL later to log in to the SageMaker Unified Studio portal and query our data across multiple engines.
Then, you create a SageMaker Unified Studio project, an integrated development environment (IDE) that provides a unified experience for data processing, analytics, and AI development. As part of project creation, an IAM role is automatically generated. This role will be used when you access SageMaker Unified Studio later. For more details on how to create a SageMaker Unified Studio project and domain, refer to An integrated experience for all your data and AI with Amazon SageMaker Unified Studio.
To implement this solution, you need a DynamoDB table that can either be used from your existing resources, or created using the sample data file that you can import from an S3 bucket. For this post, we guide you through importing sample data from an S3 bucket into a new DynamoDB table, providing a practical foundation for the concepts discussed.
To create a sample table in DynamoDB, complete the following steps:


Complete the following steps to create a DynamoDB table from a file from Amazon S3, using the import from Amazon S3 functionality. Then you can enable the settings on the DynamoDB table required to enable zero-ETL integration.


ecommerce_customer_behavior, the partition key as customer_id, and the sort key as product_id, then select Next.


It will take a few minutes for the import status to change from Importing to Completed.


When the import is complete, you should be able to see the table created on the Tables page.

ecommerce_customer_behavior table and select Edit PTIR.
This is required for setting up zero-ETL using DynamoDB as source.
On the Backups tab, you should see the status for PITR as On.

 This policy uses all the resources, which shouldn’t be used in production workload. To deploy this setup in production, restrict it to only specific zero-ETL integration resources by adding a condition to the resource-based policy.
Now that you have used the Amazon S3 import method to load a CSV file to create a DynamoDB table, you can enable zero-ETL integration on the table.
To validate if the catalog permission setting is appropriate, complete the following steps:

salesmarketing_XXX.
 The following code is an example of permissions for catalog settings:
Post Syndicated from jzb original https://lwn.net/Articles/1001773/
Nyxt is an unusual web
browser that tries to answer the question, “what if Emacs was a
good web browser?”. Nyxt is not an Emacs package, but a full
web browser written in Common Lisp and available under the BSD
three-clause license. Its target audience is developers who want a
browser that is keyboard-driven and extensible; Nyxt is also developed
for Linux first, rather than Linux being an afterthought or just a
sliver of its audience. The philosophy (as described in its FAQ)
behind the project is that users should be able to customize all of
the browser’s functionality.
Post Syndicated from jzb original https://lwn.net/Articles/1024345/
The Netdev
0x19 conference was held in Zagreb, Croatia from March 10
through March 13. The organizers announced
today that the videos and slides for all sessions are now
online. Topics from the conference include IRQ suspension, the future
of SO_TIMESTAMPING, remote TCP connection offloading, and
more.
Post Syndicated from The Atlantic original https://www.youtube.com/shorts/7vNmjxs7TkA
Post Syndicated from Bruce Schneier original https://www.schneier.com/blog/archives/2025/06/report-on-the-malicious-uses-of-ai.html
OpenAI just published its annual report on malicious uses of AI.
By using AI as a force multiplier for our expert investigative teams, in the three months since our last report we’ve been able to detect, disrupt and expose abusive activity including social engineering, cyber espionage, deceptive employment schemes, covert influence operations and scams.
These operations originated in many parts of the world, acted in many different ways, and focused on many different targets. A significant number appeared to originate in China: Four of the 10 cases in this report, spanning social engineering, covert influence operations and cyber threats, likely had a Chinese origin. But we’ve disrupted abuses from many other countries too: this report includes case studies of a likely task scam from Cambodia, comment spamming apparently from the Philippines, covert influence attempts potentially linked with Russia and Iran, and deceptive employment schemes.
Reports like these give a brief window into the ways AI is being used by malicious actors around the world. I say “brief” because last year the models weren’t good enough for these sorts of things, and next year the threat actors will run their AI models locally—and we won’t have this kind of visibility.
Post Syndicated from corbet original https://lwn.net/Articles/1024160/
The 6.16 kernel will include a number of changes to how the kernel handles
the processing of core dumps for crashed processes. Christian Brauner explained
his reasons for doing this work as: “Because I’m a clown and also I had
“. The
it with all the CVEs because we provide a **** API for userspace
handling of core dumps has indeed been a constant source of
vulnerabilities; with luck, the 6.16 work will result in rather fewer of
them in the future.
Post Syndicated from daroc original https://lwn.net/Articles/1024317/
Security updates have been issued by AlmaLinux (go-toolset:rhel8, golang, nodejs:20, nodejs:22, openssh, and python36:3.6), Debian (edk2, libfile-find-rule-perl, and webkit2gtk), Fedora (emacs, libvpx, perl-FCGI, and seamonkey), Mageia (cifs-utils), Red Hat (containernetworking-plugins, go-toolset:rhel8, golang, gvisor-tap-vsock, krb5, mod_auth_openidc:2.3, protobuf, and thunderbird), Slackware (seamonkey), SUSE (gimp, gnutls, haproxy, opensaml, openssh, openvpn, python-cryptography, python-tornado, python311-nh3, and python311-selenium), and Ubuntu (gst-plugins-bad1.0 and linux-fips).
Post Syndicated from Rapid7 original https://blog.rapid7.com/2025/06/06/cultivating-growth-and-development-at-rapid7/

At Rapid7, we’re pushing the boundaries on what a cybersecurity company can be as we work to build a more secure digital future. In a field where the threat landscape continues to evolve, continuous learning and the development of our people becomes an engine for company success and innovation. With more than a dozen offices around the world, Rapid7’s culture provides a foundation where people can grow their skills and progress in their careers, while driving meaningful impact to the business.
We sat down with three Rapid7 team members from different departments, and across our global offices, and invited them to share more about their own career growth and development. Through the experiences of Vladislav Pavlovski, Manager, Website Development, Courtney Cronin, Account Executive, Commercial, and Daniel McGreevy, Senior Technical Support Engineer, we see a consistent emphasis on teamwork, support from managers, and recognition to fuel career trajectories for Rapid7 employees around the world.
A prominent aspect of Rapid7’s culture is the accessibility of leaders and the strong mentorship opportunities available. When stepping into a leadership role to relaunch the company website, Vladislav Pavlovski highlighted how his director, Victoria Krichevsky, helped him balance development work with coordination responsibilities.
“Her feedback helped me realize that I didn’t have to do everything myself — that success meant enabling others as well,”
Vladislav said.
“Her support helped me connect the dots between day-to-day execution and longterm vision and made a big difference in how confident I felt navigating this new territory.”
This exemplifies how leaders at Rapid7 provide guidance and support that go beyond task management, focusing on broader growth.
“When I eventually moved into the Website Development Manager role, it was not only the result of the work I put in, but also the outcome of having strong, intentional support from someone who believed in the direction we were heading. That experience really shaped how I think about leadership and mentorship today,”
he said.
For Courtney, her manager also played a direct role in helping her prepare for a promotion opportunity from Sales Development Representative to Account Executive.
“I had the opportunity to meet with each of the Commercial Sales Managers to sharpen my skills as a future AE. We focused on roleplays, reviewed enablement on our products and services, introduced negotiation strategies, and refined my presentation skills. That level of investment in my development from both my current manager and the team I was looking to grow into made a huge impact, and I’m grateful for how collaborative and encouraging the team was during that transition.”
Courtney also shared how she values learning from her manager’s career growth as a woman in sales.
“I take full advantage of having a manager who started in the same role, especially as a woman in sales,”
she said.
“She understands the challenges firsthand and has been a huge influence in building my confidence. I make the most of her experience by asking for advice, learning how she navigated similar situations, and applying those lessons to my growth. Her journey and success show me what’s possible to achieve here at Rapid7, and I’m grateful to have her as both a mentor and a role model!”
Vladislav also noted,
“Leaders are accessible, and there’s a real openness to ideas from any level. It’s not about titles — it’s about potential and contribution.”
This approach makes employees feel valued and encourages them to take ownership of their development.
In addition to support from leaders, Rapid7 works to create an environment where employees can seek encouragement and guidance from peers and cross-functional partners when faced with challenges.
Daniel McGreevy started at Rapid7 as an apprentice and leveraged the expertise of his colleagues to grow his own capabilities and progress through his career.
“Working with our Technical Support experts across multiple products, and getting feedback from Support Engineers helped improve enablement across Global Support and really impacted how I approach solving complex challenges,”
he said.
Additionally, he shared how collaboration with product management and engineering teams impact product releases and ensure support is ready and equipped to assist customers effectively.
“By collaborating with different teams across the business, we’re able to improve how we service our customers while gaining additional context on the business, our products, and the goals and objectives of each of the teams we partner with and how it contributes to our bigger company initiatives.”
Incorporating this holistic view has played a role in Daniel’s progression into a Senior Technical Support Engineer.
For Vladislav, leading the launch of a new website was a significant career milestone, but what he says he’s even more proud of was the collaboration and partnership between various teams to get it over the finish line.
“The website launch was a huge project with high visibility and complex cross-functional alignment,”
he said.
“We created a space where everyone felt safe to contribute, ask for help, experiment, and make mistakes. We built trust between team members, and when people are not afraid to challenge ideas and share concerns, that openness drives better outcomes for everyone.”
The stories of Vladislav, Courtney, and Daniel paint a vivid picture of career growth and development at Rapid7. From accessible leadership and structured support to recognition and empowerment, Rapid7 fosters an environment where employees can thrive.
To learn more about working at Rapid7, visit our careers site: careers.rapid7.com
To view all open jobs, visit careers.rapid7.com/jobs/search
Post Syndicated from The History Guy: History Deserves to Be Remembered original https://www.youtube.com/watch?v=V9HzRIc4CXY
Post Syndicated from Емилия Милчева original https://www.toest.bg/tsivilizatsionniyat-izbor/

Пукнатините в коалицията, която представлява част от демократичната общност в 51-вия парламент – „Продължаваме промяната“–„Демократична България“, се превръщат в разделителни линии. В момента, в който ДБ (ДСБ, „Да, България“) се присъедини към петицията „Време е за проевропейски демократичен президент на България“, ПП обяви едностранно инициативата си за вот на недоверие към коалиционното правителство на Росен Желязков (ГЕРБ).
ДБ са резервирани към подобни действия през юли, а ПП – към общата президентска кандидатура.
Напрежението между двете политически сили расте точно когато на България ѝ предстоят съдбовни предизвикателства – още няколко крачки до пълноправното членство в еврозоната от 1 януари 2026 г. и до същинския разговор за стратегическите цели на държавата след еврото, както и ключови президентски избори. Конвергентните доклади на Европейската комисия (ЕК) и Европейската централна банка за готовността ни да приемем единната европейска валута са положителни, но окончателното решение ще дойде на 8 юли, когато Еврогрупата ще приеме законодателните решения за присъединяването на България към еврозоната.
Те са общо три: две от тях може да бъдат приети с квалифицирано мнозинство, а законодателното решение за фиксирането на обменния курс – с единодушие на 20-те държави в еврозоната плюс България. На 30 юни ЕК ще предложи обменния курс, който ще е известният на всички фиксинг 1 евро = 1,95883 лв.
„Продължаваме промяната“ обяви преди два месеца, че ще поиска вот на недоверие срещу правителството, след като излязат резултатите от конвергентните доклади, и с този аргумент не подкрепи двата неуспешни вота срещу кабинета, инициирани от eвроскептичния и проруски блок в парламента – „Възраждане“, МЕЧ и „Величие“. Не ги подкрепи и партньорът на ПП „Демократична България“. За ДБ септември е по-подходящ за внасяне на вот на недоверие – или пък „точният момент се уточнява впоследствие“.
След като президентът Радев обяви инициативата си за референдум за еврото, председателят на ДСБ Атанас Атанасов обеща подкрепа за правителството до фактическото влизане на България в еврозоната на 1 януари 2026 г.
Ние от „Демократична България“ заявки за вот на недоверие не сме дали. Трябва да мислим, преди да предприемем какъвто и да било ход. Да мислим дали има повод за нещо подобно. Да се държим като конструктивна, а не истерична опозиция.
Ивайло Мирчев, съпредседател на „Да, България“
В парламентарната демокрация вотът на недоверие е най-силният инструмент на опозицията, стига да бъдат набелязани ясно целите, които да постигне. Предишните два, внесени в 51-вото Народно събрание от „Възраждане“, МЕЧ и „Величие“, бяха използвани за шумна антиевропейска пропаганда, включително срещу приемането на еврото, въпреки че формално бяха заради външната политика и корупцията. „Възраждане“ са подготвили мотивите и за трети – за финансовата политика, също и „Величие“ – по темата екология заради незаконните сметища.
Актът на внасяне на вот на недоверие непосредствено след огромен национален успех [еврозоната – б.а.] по същността си е девалвация на вота на недоверие.
Йордан Иванов, депутат от ПП–ДБ
Вотът на недоверие е средство за реактивиране на електората и в този случай разграничаване от ГЕРБ и ДПС, с които ПП–ДБ управляваха в кабинета сглобка. Но освен несигурните политически дивиденти, в този момент има и политически рискове, като разцепление на общия фронт с ДБ, а при провал на вота – и загуба на политически авторитет, който може да настъпи още с неуспеха да се съберат необходимите 48 гласа за внасянето му. Едва ли ще се стигне до разпадане на коалицията, тъй като и двете страни разбират огромните рискове и електорален спад, с които ще се сблъскат. Но напрежението остава.
Трябва да инициираме вот на недоверие, иначе ще бъде тиха подкрепа за управление на Пеевски.
Кирил Петков, съпредседател на ПП
В крайна сметка от ПП заявиха, че след 9 юли ще започнат да събират подписи, за да внесат вота. „След тази дата, когато членството в еврозоната става необратим процес, ще започнем работа по другата ни голяма цел – да чистим корупцията“, заяви Петков. ПП разполагат със 17 депутати, а изискването за внасяне на вот на недоверие е за 48 – минимум ⅕ от народните представители. ПП ще се обърнат най-напред към ДБ, а след това и към националпопулистките и проруски формации, чиито вотове на недоверие досега не подкрепяха, както и към ДПС–ДПС на Доган.
Председателят на МЕЧ Радостин Василев прогнозира политическа нестабилност след потвърждението за еврото и заяви, че подписи просто така не дават:
Очаквам да дойдат, да кажат на каква тема ще е вотът, ако можем да направим общ вот на обединената опозиция.
От „Възраждане“ засега не дават надежди за съгласие за третия вот на недоверие към кабинета „Желязков“.
Ние ще подкрепим всеки внесен вот на недоверие, но няма как да си сложим подписите с лицата от ПП, към които изпитваме, меко казано, отвращение.
Костадин Костадинов, лидер на „Възраждане“
За да бъде съборено правителството, е необходимо абсолютно мнозинство от 121 народни представители. ПП, ДПС–ДПС, МЕЧ, „Величие“ и „Възраждане“ разполагат с 89. Тоест за да падне правителството, трябва да гласуват и от ДБ, и от ДПС – Ново начало. Ако партията на Пеевски не подкрепи вота, тъй като лидерът олигарх често повтаря мантрата, че работи за стабилно правителство, ПП ще застане до Радев и „Възраждане“, както отбеляза и Бойко Борисов.
Ако мине вотът на недоверие, те трябва да се притесняват. Защото ако успее, ПП ще се наредят до „Възраждане“, „Величие“, МЕЧ. И до Радев. С кое е допринесъл [Кирил Петков – б.а.]? Че тревожи Брюксел, че може да падне правителството и внася вот на недоверие? Това звучи гротескно. Кирил Петков остава зад борда. Той трябва да обясни на своите хора защо трябва да падне това правителство, за да има преформатиране и да дойде „Възраждане“ или Радев.
Ходът на ПП би имал здрав смисъл само при обща стратегия на коалицията, в която участват, че предсрочни избори са по-добър вариант от статуквото, и когато партиите са изяснили кои биха могли да бъдат техни партньори в управлението и при какви условия. В случай че бъдат предизвикани избори наесен, те ще са доминирани от кампанията срещу еврото точно преди финала на процеса. А с обещания контрол върху спекулативни повишения на цените ще трябва да се заеме едно служебно правителство, оглавено, защо не, от председателката на парламента Наталия Киселова.
В последните месеци различията между ПП и ДБ ясно се проявяват. Например в реакциите им към референдума за еврото, предложен от президента Радев на 9 май. От страна на ПП, чиито лидери бяха министри в служебен кабинет на президента, коментарите бяха сдържани. Кирил Петков определи искането за референдум като „една голяма грешка“, Асен Василев избра технократския стил на говорене в подкрепа на еврото, не и атаки към Радев.
В ДБ бяха значително по-критични. Запитаха дали инициативата за референдум не е заради разследването по аферата „Боташ“, с която България губи милиарди долари, и критикуваха държавния глава в опит за дестабилизация и действия срещу националните интереси.
Президентът междувременно намекна за политически проект и така катализира инициативата за предварителни избори за кандидат-президент на демократичната общност 17 месеца преди вота за държавен глава.
ДСБ бяха първи с предложението за първични избори, но в името на общественото начало идеята получи гражданственост сега. Ползите са значителни – стига първичният вот да успее да излъчи кандидат с потенциал за по-висока подкрепа от тези 400 000–500 0000 гласа, които може да мобилизира демократичната общност. (Тези гласове, както отбеляза политологът Огнян Минчев в коментар във Facebook, ще се окажат недостатъчни дори за класиране на общия кандидат за балотаж.) Активността на президентски избори е значително по-висока, отколкото на парламентарни. На балотажа за държавен глава през 2016 г. гласуваха над 3,5 млн. души, а през 2022 г. бяха с над 780 000 по-малко, спечелен за втори път от Румен Радев и Илияна Йотова.
Тоест ако се стигне до общ проевропейски кандидат, той се нуждае от почти двойно повече гласове от присъщите на общността. Това означава, че партийната идентификация е (почти) изключена.
Първо, издигането на общ кандидат ще създаде по-голямо доверие и емоционална връзка с избирателите. Част от тях са разочаровани от разпадналата се вече сглобка с Пеевски–Борисов. Други очакват ясна алтернатива и смелост за противопоставяне на статуквото.
Второ, ще заздрави, но и ще контурира известната с фрагментацията си демократична общност. Кой е част от тази общност, идеологията включена ли е в критериите, или принадлежността се определя според моментна политическа целесъобразност, ситуационни съюзи и врагове?
Трето, в стратегически план ще зададе тон и платформа за бъдещи (коалиционни) партньорства. На последната си национална конференция „Да, България“ вече заяви своите намерения за изграждане на ясна проевропейска и реформаторска сила, готова да води, а не просто да участва в обединения. Настоящето с ПП се нуждае от надграждане.
В обращение е хипотезата, че ПП държат на бившия премиер Николай Денков за свой кандидат и не биха се съгласили с ДБ. Но през 2022 г. ПП прие предложението на ДБ за обща кандидатура за кмет на София, което донесе победа (макар и трудна) на Васил Терзиев на балотажа.
Трябва да имаме максимално обединение на демократичните общности и там, където е възможно – един кандидат. Там, където може с ДБ и други обществени и партийни организации, които изповядват нашите ценности.
Кирил Петков, 19 ноември 2022 г., Нова телевизия
Възможно ли е да бъде повторен успехът от 1996 г., когато излъчените от Обединените демократични сили Петър Стоянов – Тодор Кавалджиев спечелиха балотажа? В своя резолюция ДСБ отбелязват, че именно „успехът от 1996 г. показва, че този подход носи реална мобилизация и висока обществена легитимност“. Но този успех се дължеше не само на обединението, а и на тоталния крах на управлението на БСП – зърнената криза, причинена от безконтролния износ, банковите фалити, инфлацията, грабежа и тоталната липса на законност, протестите.
Разбира се, роля изигра също и профилът на неизвестния дотогава юрист Стоянов – европеец по възпитание и изказ, с умерен и почтен политически образ, далеч от партийния цинизъм на Прехода. Той беше фигура, способна да въплъти вярата в ново начало, без да поляризира. Подкрепата му беше не само партийна, а и социална – обединена около идеята за цивилизационен избор и категоричен отказ от онова, което олицетворяваше властта на БСП.
Близо 30 години по-късно България е постигнала мечтите на онази демократична общност – член е на ЕС и НАТО, а от 1 януари 2026 г. предстои да се присъедини и към еврозоната. Сега заплахите са други, а енергията – колкото е останала в застаряващото българско общество – лесно се манипулира и насочва в посоки, чужди на националните интереси . Методите са известни – дезинформация, външно (руско) влияние и вътрешна апатия, които подкопават доверието в институциите и демократичния процес.
Големият въпрос пред демократичната общност е каква да бъде формулата за бъдещия кандидат – с по-изразен либерален профил или по-приглушен, предвид трудната задача да бъдат мобилизирани поне един милион избиратели, загрижени за европейското бъдеще на България. Срещу него ще има поне двама кандидати на консервативната вълна – на русофилите патриоти от „Възраждане“ и сие и на народняците от ГЕРБ и присъдружията им. Кого ще подкрепи ДПС – Ново начало, е рано да се каже, въпреки че сега е лесно да се направи, предвид схватките на Пеевски с Костадинов и предложението му да се свалят имунитетите на четиримата депутати от „Възраждане“, вандализирали Дома на Европа в София.
Демократичната общност не може да си позволи лукса да търси кандидат просто „анти-Радев“ или „анти-Костадинов“. Нужно е лице, което вдъхва надежда, интегрира отвъд партийното ядро, комуникира ясно европейската посока и не се страхува да назове опонентите си.
Ако някога е имало момент, в който залогът е бил повече от избор на президент, това ще е през есента на 2026 г., когато ще се решава дали България ще се придвижи напред по европейския път, или ще бъде подложена на още по-дълбока ерозия отвътре.
Post Syndicated from Йоанна Елми original https://www.toest.bg/glasovete-na-amerika-broy-2/

Едно време всички баби гледаха сериали. Сигурно още гледат. Но едва сега, като зрял човек, който цени разказването на истории и дори понякога се опитва да го прави, мога да оценя тънкото изкуство на сапунката.
Половин час гледане на който и да е епизод на сериала стига, за да се запознае човек с всички герои, да отгатне кой каква връзка има с друг, да си избере любимец, да намрази злодеите и да провери в програмата кога е следващият епизод, за да не пропусне развитието.
Но дори и да се изпусне повече от един епизод, упражнението просто се повтаря, защото такъв е гениалният дизайн на сапунката – верига от циклични микроразкази, които никога не омръзват. Така човек може да не е гледал повече от половината сериал, но да знае точно какво се случва. И дори да предскаже събитията с относителна точност.
Е, нещо такова е и американската политика.
Последната седмица донесе очакван обрат: двама от главните герои охладняха един към друг и дори си размениха остри реплики. В крайна сметка в никой класически сюжет няма място за двама главни герои, освен ако не са влюбени, разбира се. След като парализира или напълно премахна множество от държавните агенции, които разследваха бизнесите му, милиардерът Илън Мъск обяви, че напуска властта, за да се фокусира върху компаниите си. На разлъка разкритикува проектобюджета на президента Тръмп, наричайки го „гнусно недоразумение“.
Според независимата Бюджетна агенция на Конгреса „Големият красив законопроект“ на президента Тръмп ще увеличи националния дълг с 2,4 трлн. долара. Това може да се окаже проблем за републиканците, за които намаляването на дълга е основен приоритет от години. Естествено, ако допуснем, че е възможно да се мисли извън партийната линия, във факти и реалности, което също е проблем за републиканците. Вече тече активна кампания, според която експертите, позволяващи си волности, като критичност и обективни оценки, лъжат народа и са част от световната конспирация. Отново – предвидимо. На всички е ясно, че са прави само онези експерти, които са съгласни с нас.
Илън Мъск вече подстрекава избирателите да звънят на своите представители, за да стопират законопроекта. Няма как да не го кажа: въпреки че понякога е ужасно глупава, демокрацията все пак продължава да бъде красива.
Подробна разбивка на спестяванията и разходите, ако законопроектът бъде приет в този вид, може да бъде видяна тук. За потребителите, които не си падат по аргументирани обяснения или „мейнстрийм медии“, ето какво казва изкуственият интелект „Грок“ на Мъск:

Сред другите постижения на администрацията от последните дни и седмици са над 2500 медицински изследвания с орязано или напълно спряно финансиране. „Хората трябва да знаят, че се спират проучвания, които вероятно биха подкрепили – казва пред „Ню Йорк Таймс“ д-р Идън Танър, химик от Университета в Мисисипи. – Бих искал да открия лечение за рака на мозъка. Не мисля, че в това има нещо кой знае колко скандално.“
Трябва да се пестят пари, особено държавни. От началото на президентството си семейство Тръмп е увеличило богатството си с милиарди. Но в крайна сметка не може само да се работи, човек трябва и да си угажда. Президентът до такава степен отговаря на американския идеал за себереализация и уповаване на частния капитал, че дори сам си подсигури самолет. Може обаче да се окаже, че администрацията е поискала самолета от Катар, а не е точно подарък, както съобщиха в началото. Някой може да сметне това за леко awkward или криндж, както казват младите, но всъщност е the art of the deal (от „Изкуството на сделката“ – книгата и слоганът, с който е известен настоящият президент). А президентът и бездруго каза, че този самолет му е прекалено голям.
Междувременно през април администрацията на Тръмп се закани, че за 90 дни ще сключи 90 търговски сделки с 90 държави – нещо като 800-те дни на Сакскобургготски, но по американски. Дотук е сключена цифром и словом една сделка, но е само юни, а и винаги можем да отхвърлим реалността с аргумента, че мейнстрийм медиите лъжат, и да си измислим друга – докато не се наложи да напазаруваме в магазина, където тази седмица може да няма яйца или когато има, цените да са като за реплики на Фаберже. Но пък баба ви само яйца е яла в миналото, към което Америка трябва да се върне, за да бъде велика отново. Ако нещата стават все по-автентични, значи вървим към успех.*
Сега сериозно: през април инфлацията се забавя съвсем леко, но непредвидимостта на администрацията не позволява стабилни икономически прогнози, казват експерти. Митата вече се отразяват в повишение на цените на някои стоки, а производителите започват да вдигат цените за крайния потребител. Сред ключовите стоки, които се следят като индикатор за добра икономика и покупателна способност, през май са се вдигнали цените на яйцата, пилешкото, мляното говеждо и портокаловия сок, цената на хляба е стабилна, а беконът леко е поевтинял – като няма яйца, да ядат бекон.
Заради митата над стоманата се очаква поскъпване на строителните материали и автомобилите. Някои мита остават в сила дори след като съдът се произнесе, че Тръмп може би е превишил правомощията си. Ако човек обаче иска да разбере кои мита точно, трябва да проверява ежедневно. Но ежедневната проверка вече се е превърнала в общ навик, тъй като президентът си мени мнението бързо – все пак е зодия Близнаци, а на 14 юни отбелязваме рождения му ден с първи по рода си военен парад. Освен ако дотогава не реши нещо друго.
Наясно със ситуацията са само твърдите поддръжници на президента, които също променят мнението си със завидна гъвкавост спрямо актуалните сюжети. Но това може само да предизвика възхита, защото тази вяра издава таланта на Тръмп да прави политика. Или пропаганда. Или пък по малко и от двете. И при латиноамериканските сериали човек рядко помни какво точно е станало в предишния епизод, затова винаги му е интересно. Актуалните социологически проучвания показват около 50% неодобрение и между 46% и 49% одобрение. Кучетата си лаят, сериалът си върви.
Хубаво е, че американската политика може да разчита на силна, витална опозиция с ясно изграден план за (противо)действие. Това ни разкрива най-малкото заглавие в Newsweek, което гласи: „Колко представители на демократите са умрели от началото на политическия сезон?“ Отговорът е трима, а за позналите правилно има предвидено по едно яйце. Да знаете, че последното си го измислих, защото напоследък ни е трудно да различаваме реалност от нереалност, а и всички са станали ужасно обидчиви.
Анкета показва, че избирателите на демократите предпочитат популистки послания, като например борба срещу монополите на корпорациите и концентрацията на богатство пред „плановете за изобилие“, вероятно защото не са разбрали какво точно означава последното, което, общо взето, резюмира политическите послания на Демократическата партия. Междувременно много корпорации не празнуват и не подкрепят Месеца на прайда тази година, а данни показват, че американците започват да се усещат, че поставянето на определено знаме върху корпоративното лого и използването на „правилните“ думи и местоимения поради страх от онлайн линч може би не успява да реши нито проблема с равноправието, нито този със свободата.
За домашно от предишния път ни останаха данъчните реформи и цените, които вече засегнахме. В случай че още не сте разбрали за войните в Украйна и Израел, които президентът обеща да прекрати за отрицателно време, в истинския дух на бавните новини и на мисията на „Тоест“ ще ви съобщя, че и двете все още продължават.
Президентът Тръмп обяви, че Путин му съобщил, че ще отмъсти на Украйна за атаките в края на май, които унищожиха значителна част от руските ядрени бомбардировачи и ще останат в историите като една от най-впечатляващите военни операции. Добре, Владимир, изглежда е казал президентът Тръмп, защото обществото не научи повече. Вероятно се разбират добре, защото Путин има Луна в Близнаци; в следващ бюлетин може да предложим и синастрия.
Не че американският президент се слави с пословично търпение – екипът му обмисля да му прави брифинги като риалити шоу, защото хич не обичал да чете – но агресивната кампания по изтребването на населението на Газа зад паравана на антитероризма явно вече е неудобна дори на САЩ, защото в последните седмици се наблюдава охладняване в отношенията с Израел и лека смяна на тона, което не попречи на САЩ да наложат ново вето в ООН. Разбира се, по-вероятната причина е промяна в политиката на страната спрямо Иран и цялостното преориентиране на ролята на Америка в Близкия изток, където Тръмп наскоро държа съвсем нелоша реч със заявки за промяна във външната политика в региона, което има потенциал да бъде част от конструктивно наследство. Такъв потенциал имаха и редица други политики на Тръмп, но както винаги, изпълнението е по-сложна работа.
А на образованието ще посветим следващия брой.
Споменаваме яйцата полуиронично, защото са политическа басня с поука и добра илюстрация за настоящия политически и медиен климат.
Цената на яйцата се превърна в тема през последните месеци на президентската кампания, когато Джо Байдън все още беше на власт, въпреки че определянето на цените няма нищо общо с това кой е президент, а се влияе от много по-сложни фактори.
Тръмп обеща 50% спад на цената на яйцата, но въпреки тези обещания тя достигна рекордни нива. В началото на май прорепубликанската Fox News публикува материал със заглавие „Цената на яйцата е спаднала с 61% от началото на управлението на Тръмп“. Отвъд заглавието обаче става ясно, че понижението на пазарните цени е в резултат на „слабото търсене и спад на случаите на птичи грип“, както и на внос от Турция, Бразилия и Южна Корея плюс уравновесяване между цените на едро и пазарните цени. Статията на Fox не казва каква конкретно е ролята на президента за промените в пазара, защото както Джо Байдън, така и Тръмп няма никаква власт над яйцата (което би било добра идея за герой на Marvel или DC). От другата страна пък демократите също опитаха да извлекат политически дивидент от яйцата, например с отворено писмо до Тръмп, а много медии използваха случая за провокативни заглавия, които да хвърлят по някое виртуално яйце към президента.
Trump: "Eggs have come down 400 percent. Everybody has eggs now. They have eggs for breakfast again." pic.twitter.com/xBlS15Jvob
— Aaron Rupar (@atrupar) June 5, 2025
Яйца за всички, навсякъде, наведнъж.
И разбира се, поантата – от януари насам президентът Тръмп повтаря, че цените на яйцата падат. Заглавието на CNN резюмира финала на баснята (и политическата стратегия на Тръмп) най-добре: „Фикцията на Тръмп става реалност“. Бих добавила едно „в редки случаи“. Този път за доброто на потребителя.
Останалото е просто зрелището на политиката, което трябва да понасяме спокойно, с критична мисъл, и както в този случай – с щипка хумор.
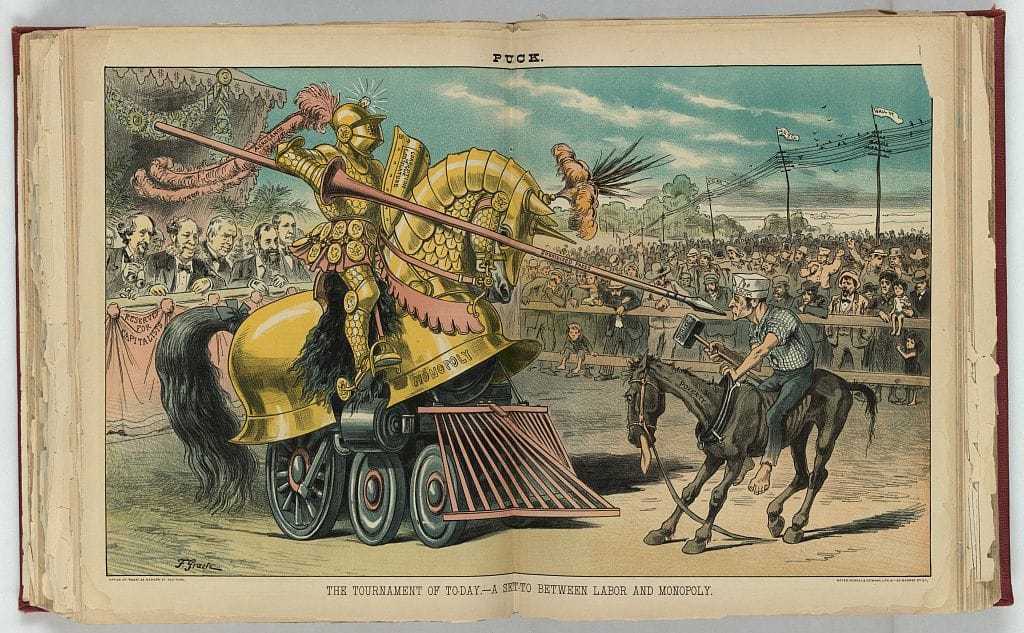
Карикатурата изобразява схватка между огромен рицар на златен кон с надпис „Монопол“. Върху перото на шлема му пише „арогантност“, върху щита – „корумпирано законодателство“, а върху копието – „субсидирана преса“. Босият му опонент работник язди „бедността“ и държи в ръката чук с надпис „стачка“. Местата вляво са „запазени за капиталисти“, а между тях виждаме Уилям Вандербилт и Джон Роуч, магнати от т.нар. Позлатена епоха, период на висока концентрация на богатство и огромни неравенства от историята на САЩ.
Абонирайте се, за да получавате този бюлетин на електронната си поща в момента, в който излезе!
Вече сте регистриран потребител на Toest.bg? Може директно от настройките на бюлетините в своя профил да изберете „Гласовете на Америка“ или да натиснете бутона по-долу:
Още нямате профил в Toest.bg? Регистрирайте се само с няколко клика:
Post Syndicated from Rapid7 original https://blog.rapid7.com/2025/06/06/indias-cyber-leaders-prepare-for-ai-driven-threats/

As India’s economy rapidly digitizes, cybersecurity challenges are becoming increasingly complex. This May, Rapid7 launched our inaugural Global Security Day series across India, bringing together top security leaders in Mumbai, Delhi, and Bengaluru to address the most pressing cyber threats facing organizations in 2025.
Across all three cities, several critical themes emerged that are shaping India’s cybersecurity landscape:
AI is No Longer Optional: Organizations recognize that AI has become essential for threat detection, exposure management, and SOC operations. The question is no longer whether to adopt AI, but how to implement it effectively.
Attack Surface Explosion: Cloud misconfigurations, insecure APIs, and identity misuse are driving today’s biggest risks. Organizations are struggling to maintain visibility and control across increasingly complex environments.
SOC Modernization is Urgent: Traditional Security Operations Centers need fundamental transformation, with automation and AI at their core to handle the volume of modern threats.
Talent Gap Challenges: Upskilling and reskilling initiatives are critical to closing the cybersecurity talent gap that’s affecting organizations globally, but particularly acutely in India’s booming tech sector.
Regulatory Evolution: India’s evolving cybersecurity regulatory landscape is shaping how organizations approach their security investments and strategy development.
Our three-city roadshow, organized in collaboration with Information Security Media Group (ISMG), focused on the theme “2025 Cyber Threat Predictions: AI-Driven Attacks, Ransomware Evolution, and Expanding Attack Surface.” The response from India’s cybersecurity community was overwhelming, with 138 security leaders and delegates participating across all three cities.
Our Mumbai kickoff set the tone for the entire series, drawing 43 security leaders eager to dive into critical cybersecurity challenges. Rob Dooley, General Manager APJ, welcomed attendees before Regional CTO Robin Long delivered comprehensive insights on:
The highlight was our fireside chat featuring Starlin Ponpandy, CISO of Orion Systems and Rapid7 customer, discussing ‘Building a New-Age SOC: Practical Applications of AI’. The conversation explored choosing the right SOC model, building effective teams, and navigating the complexities of AI trust and explainability.
The main focus of the Q&A was the evolving cyber threat landscape and how organizations can prepare for 2025’s AI-driven, increasingly complex attack environment.
The conversation was dominated by leaders sharing insights on the rise of AI-powered threats, the shift in ransomware tactics to double and hybrid extortion and the urgent need for proactive threat exposure management. Rapid7’s emphasis on real-time, AI-enabled defenses and automated risk management strategies sparked strong engagement.
Our Delhi event brought together 43 delegates for candid, strategic discussions about 2025’s top cyber threats. Security leaders engaged in deep conversations about AI-powered detection and defense, proactive exposure management, and building resilient SOCs with automation.
The panel discussion on ‘Building a New-Age SOC’ addressed critical challenges including the cybersecurity talent gap and integrating security into DevOps workflows, a thought-provoking conversation examining identity-centric security models and the shift from traditional SOCs to Managed Detection and Response solutions.
Attendees posed incisive questions about upskilling teams in an AI-driven environment, managing tool sprawl, and operationalizing security by design – highlighting the sophisticated thinking of India’s cybersecurity leadership.
Our Bengaluru finale drew the largest crowd with 52 delegates, including CISOs and cybersecurity executives from across South India. The discussions were highly tactical, focusing on:
Veteran industry speaker Satish Kumar Dwibhashi joined Robin Long for discussions that reinforced a clear theme: security strategy must evolve in lockstep with attacker innovation.
The success of our India Security Days reflects not just the hunger for cybersecurity knowledge in the region, but also Rapid7’s commitment to supporting India’s digital transformation journey. We’re excited to announce that we’re expanding our presence with aGlobal Capability Center (GCC) in Pune, which will serve as a hub for innovation and home to teams across engineering, business support, and our Security Operations Center (SOC).
This initiative represents more than just business expansion – it’s about building cybersecurity capability and expertise right here in India, that will shape a secure digital future for organizations around the world.
The conversations, connections, and insights from our India Security Days have reinforced our belief that India’s cybersecurity community is among the most forward-thinking globally. The challenges are significant – from AI-powered attacks to evolving ransomware tactics – but so is the talent, innovation, and determination to address them.
As we look toward 2025 and beyond, events like these remind us that cybersecurity is ultimately about people: the security leaders making tough decisions, the practitioners implementing defenses, and the communities sharing knowledge and supporting each other.
Thank you to all the security leaders who joined us in Mumbai, Delhi, and Bengaluru. Your engagement, questions, and insights made these events truly impactful. We look forward to continuing these conversations and supporting India’s cybersecurity community as we navigate the challenges and opportunities ahead.
Interested in joining our growing team in India? Learn more about career opportunities at our new GCC in Pune.
Post Syndicated from Kirankumar Chandrashekar original https://aws.amazon.com/blogs/devops/access-claude-sonnet-4-in-amazon-q-developer-cli/
Amazon Q Developer now supports Claude Sonnet 4 within the CLI, bringing advanced coding and reasoning capabilities to your development workflows at no additional cost. This latest model excels in coding with a state-of-the-art 72.7% for agentic coding on the SWE-bench (see Claude 4 announcement for more information). With enhanced coding and reasoning capabilities, it helps you analyze complex code, optimize everyday development tasks, implementing bug fixes, running bash commands, and developing new features with immediate feedback loops and more precise responses.
To help you leverage Claude Sonnet 4, Amazon Q Developer lets you easily select specific Claude Sonnet models, giving you increased flexibility the CLI.
For detailed information about Claude model capabilities and comparison, refer to the Anthropic models overview.
In this blog, I will show you how to select Claude Sonnet 4 as your model within the Q Developer CLI and then walk you through a quick demo.
Make sure to update to the latest version (v1.11.0 onwards) of Amazon Q Developer CLI. Refer installing Amazon Q for command line for installation instructions. You can access Claude Sonnet 4 through these options:
/model command and select claude-4-sonnetq chat --model claude-4-sonnetq settings chat.defaultModel claude-4-sonnet.The supported model names for the --model parameter and settings are:
claude-3.5-sonnetclaude-3.7-sonnet (default)claude-4-sonnetQ Developer CLI selects models in the following order:
/model or --model)Claude 3.7 Sonnet)The Q Developer CLI agent defaults to Claude 3.7 Sonnet when no specific model is selected. During active chat sessions, you can seamlessly switch between models using the /model command. Chat continuity is maintained across sessions, with the system retaining the previously selected model when conversations are resumed. If you prefer Claude Sonnet 4, setting it as the default model in user settings will automatically apply to all new chat sessions, though this can be overridden with specific model selections as needed.

Figure 1: Q Developer CLI showing the model loaded for the session
After switching to Claude Sonnet 4 in Q Developer CLI, let’s explore its capabilities with a practical coding example. Here’s the prompt I’ll use for this demonstration:
Create a Python command-line to-do list app with these features:
- Add tasks with descriptions and priorities (low/medium/high)
- Mark tasks as complete by index
- Display tasks sorted by priority, then insertion order
- Show completion status ([x] done, [ ] pending)
- Handle errors for empty tasks and invalid indices
- Store tasks in memory only
Please provide the code to implement this application.

Figure 2: Q Developer CLI interface showing Claude Sonnet 4 in action
In the above demonstration, Q Developer CLI with Claude Sonnet 4 went beyond what was asked in the provided requirements in the prompt by implementing sophisticated command parsing with quoted descriptions, comprehensive error handling, and clean object-oriented design enhanced by type hints. The interface features a helpful guidance system with clear error messages, elegant enum-based priority management, and formatted output for clear task representation.
Additionally, Q Developer CLI with Claude Sonnet 4 also generated documentation in the README for the to-do application, including practical error handling examples and clear usage instructions – transforming the prompt requirements into a well-structured, user-friendly application.
The availability of Claude Sonnet 4 represents a significant advancement in Amazon Q Developer’s capabilities. From intricate code refactoring to streamlined documentation creation, Claude Sonnet 4 helps you accomplish both complex and routine development tasks efficiently.
Whether selecting Claude Sonnet 4 for complex tasks or using other models for specific needs, Amazon Q Developer adapts to your preferences, optimizing AI assistance while maintaining efficiency in your workflow.
The latest version(v1.11.0) of Amazon Q Developer awaits in the CLI, ready to support your development journey with enhanced model capabilities and selection options. Refer Installing Amazon Q for Command line for installation instructions.
To learn more about Amazon Q Developer’s features and pricing details, visit the Amazon Q Developer product page.

Kirankumar Chandrashekar is a Generative AI Specialist Solutions Architect at AWS, focusing on Amazon Q Developer. Bringing deep expertise in AWS cloud services, DevOps, modernization, and infrastructure as code, he helps customers enhance their development workflows using Amazon Q Developer. Kirankumar is passionate about solving complex customer challenges and enjoys music, cooking, and traveling.
Post Syndicated from Betty Zheng (郑予彬) original https://aws.amazon.com/blogs/aws/now-open-aws-asia-pacific-taipei-region/
Today, Amazon Web Services (AWS) announced that AWS Asia Pacific (Taipei) Region is generally available with three Availability Zones and Region code ap-east-2. The new Region brings AWS infrastructure and services closer to customers in Taiwan.

Skyline of Taipei including the Taipei 101 building
As the first infrastructure Region in Taipei and the fifteenth Region in Asia Pacific, the new Region expands the AWS global footprint to 117 Availability Zones across 37 geographic Regions worldwide. The new AWS Region will help developers, startups, and enterprises, as well as education, entertainment, financial services, healthcare, manufacturing, and nonprofit organizations run their applications and serve end users while maintaining data residency in Taiwan.
AWS in Taiwan
AWS has maintained a presence in Taiwan for more than a decade, starting with the opening of the AWS Taipei office in 2014. Since then, AWS has introduced many infrastructure offerings in Taiwan including:
In 2014, AWS launched the first Amazon CloudFront edge location and added another in 2018, offering customers a secure and efficient content delivery network for accelerating data, video, application, and API delivery worldwide.
In 2018, AWS established two AWS Direct Connect locations in Taiwan to enhance connectivity options. With the launch of the AWS Asia Pacific (Taipei) Region, we’ve added a new Direct Connect location in Taiwan to provide customers with higher speed and bandwidth.
In 2020, AWS launched AWS Outposts in Taiwan, helping customers seamlessly extend AWS infrastructure and services to their on-premises or edge locations for a consistent hybrid experience.
In 2022, AWS launched AWS Local Zone in Taipei to support low-latency applications requiring single-digit millisecond responsiveness.
Today, with the launch of the AWS Asia Pacific (Taipei) Region, we further strengthen our commitment to support innovation in Taiwan. Organizations in regulated industries will be able to store data locally while maintaining complete control over data location and movement. From high-tech manufacturing to semiconductor companies and small and medium enterprises (SMEs), businesses will gain access to the scalable infrastructure needed for growth and innovation.
AWS customers in Taiwan
Organizations across Taiwan are already using AWS to innovate and deliver differentiated experiences to their customers, for example:
Cathay Financial Holdings (CFH) is a leader in financial technology in Taiwan. It continuously introduces the latest technology to create a full-scenario financial service ecosystem. Since 2021, CFH has built a cloud environment on AWS that strengthens its security control and meets compliance requirements.
“Cathay Financial Holdings will continue to accelerate digital transformation in the industry, also improve the stability, security, timeliness, and scalability of our financial services,” said Marcus Yao, senior executive vice president of CFH. “With the new AWS Region in Taiwan, CFH is expected to provide customers with even more diverse and convenient financial services.”
Gamania Group is revolutionizing the entertainment landscape by integrating AI with celebrity IP through their innovative Vyin AI platform. Gamania utilized the robust and scalable infrastructure of AWS to develop secure, responsive AI interactions.
Benjamin Chen, chief strategy officer and head of Innovation Lab, said: “The core goal of Vyin AI is to create a digital identity that is fully interactive, lifelike, and safe to use. This demands technologies that are stable, responsive, and secure. To that end, we rely on the robust and resilient cloud infrastructure of AWS, and look forward to the low-latency advantages offered by the AWS Region in Taiwan. AWS provides a highly stable and secure environment for Vyin AI to provide users with secure and AI hallucination free interactions. AWS Cloud services allow us to focus more on core AI technology innovation and the enhancement of the ‘hyper-personalized interactive’ user experience, thereby accelerating product iteration and optimization.”
Chunghwa Telecom is a leader in cloud network services in Taiwan with the broadest mainstream 5G bandwidth, exceptional network speed, and globally recognized mobile internet capabilities. Chunghwa Telecom utilizes generative AI platforms such as Amazon Bedrock to build innovative services and create intelligent applications for various industries.
Dr. Rong-Shy Lin, president of CHT, stated: “With the launch of the AWS Region in Taiwan, CHT’s partnership with AWS has entered a new phase. We will deepen the integration of key advantages of the AWS Region, such as low latency and local data storage, combining them with CHT’s extensive backbone network, rich cloud experience, and professional team that has obtained multiple AWS Competency certifications. This will allow CHT to provide solutions that meet strict security and compliance requirements for government, financial, critical infrastructure, and highly regulated industries. At the same time, we are utilizing AWS technologies such as Amazon Bedrock to develop innovative applications and accelerate digital transformation and AI adoption. We will continue to provide optimized cloud and network services in Taiwan while supporting customers’ global expansion.”
AWS Partners in Taiwan
The AWS Partner Network in Taiwan plays a crucial role in helping customers adopt cloud technologies and maximize value from the new AWS Asia Pacific (Taipei) Region. These specialized partners combine deep technical expertise with local market knowledge to accelerate digital transformation across industries.
eCloudvalley Digital Technology Group is an AWS Premier Tier Services Partner with a team of cloud experts with more than 600 certifications.
“eCloudvalley Group has always embraced our mission of being a cloud evangelist, driving the adoption of cloud technology across Taiwan’s industries,” said MP Tsai, chairman of eCloudvalley Group. “With over a decade of close collaboration with AWS, we are honored to help more and more customers and industries move to the cloud while being part of customers’ digital transformation journey on AWS. We believe that the launch of the AWS Asia Pacific (Taipei) Region will further support Taiwan companies’ digital transformation and innovation in Taiwan with its world-leading cloud technology, while industries with higher local data residency requirements, such as finance and healthcare, will be able to further advance their cloud transformation journey.”
Nextlink Technology Inc. is an AWS Premier Consulting Partner, certified Managed Service Provider (MSP) and has AWS Level 1 Managed Security Service Provider (MSSP) and Government Consulting Competency.
“The investment of AWS in local infrastructure will help drive the digital transformation of Taiwan companies, boosting the development of various industries spanning from traditional industries to emerging digital sectors,” said Shasta Ho, the CEO of Nextlink Technology Inc. “We look forward to continuing working with AWS to help enterprises across industries deeply utilize the new AWS Asia Pacific (Taipei) Region. This local advantage will address customer needs in data localization, low latency, compliance, and high performance computing workloads. We also look forward to using AWS world-leading cloud technologies to power customers’ digital transformation journeys while contributing to the diversification of Taiwan’s economy.”
SAP has been a strategic partner of AWS for more than a decade, with thousands of enterprise customers worldwide running their SAP workloads on AWS.
“SAP is thrilled to see AWS establish new data centers in Taiwan,” said George Chen, SAP global vice president and managing director for Taiwan, Hong Kong, and Macau. “This investment provides Taiwan enterprises with greater choice, lower service latency, and enhanced operational flexibility. As a long-term strategic partner, SAP is committed to accelerating cloud transformation for these businesses. Through RISE with SAP, we can help customers seamlessly migrate to the cloud, enjoying greater flexibility, scalability, and reduced operational costs. By combining SAP’s enterprise solutions with the robust cloud platform of AWS, we’ll jointly empower Taiwan’s enterprises to unlock innovative AI applications and run their core businesses securely and reliably locally, driving Taiwan enterprise cloud transformation together.”
Supporting sustainable innovation in Taiwan
As Taiwan progresses toward its goal of net-zero emissions by 2050, AWS Cloud solutions are empowering organizations to enhance operational efficiency while reducing environmental impact. The new AWS Asia Pacific (Taipei) Region incorporates the AWS commitment to sustainability, helping organizations meet both technical and environmental objectives.
Ace Energy is a pioneer in Taiwan’s energy management sector. Since 2013, Ace Energy has been using AWS services such as Amazon Simple Storage Service (Amazon S3), Amazon Elastic Compute Cloud (Amazon EC2), and AWS IoT Core to provide innovative energy solutions through their Energy Saving Performance Contract model. Ace Energy has deployed energy management solutions across 1,000 locations, helped a semiconductor manufacturer reduce steam consumption by 65 percent, achieved 22 million new Taiwan dollars in annual energy savings, and decreased carbon emissions by 8,000 tons through their waste heat recovery technology.
Taiwan Power Company (Taipower) is Taiwan’s state power utility and has revolutionized its operations through AWS since 2018. By implementing smart grid technologies with drones, robotics, and virtual reality for smart patrol, Taipower has enhanced customer experience through the “Taiwan Power” application. The company has improved operational efficiency through data-driven decision-making and earned six consecutive Platinum Awards in the Corporate Sustainability category at the Taiwan Corporate Sustainability Awards.
Building cloud skills together
Since 2014, AWS has built comprehensive programs for cloud education and skills development in Taiwan. For example, educational programs such as AWS Academy, AWS Educate, and AWS Skill Builder have helped train more than 200,000 people in Taiwan on cloud skills. These programs will expand alongside our infrastructure investments to build a foundation for Taiwan’s digital future.
Taiwan boasts a vibrant AWS community that welcomes your involvement. Take part in knowledge-sharing and networking at local AWS User Groups in Taipei, engage with the four celebrated AWS Heroes in Taiwan, or consider becoming part of the growing community of AWS enthusiasts by joining the ranks of the 17 AWS Community Builders already contributing to Taiwan’s cloud ecosystem. All these community connections provide valuable opportunities to accelerate your cloud journey through local expertise and collaborative learning.
Stay tuned
The AWS Asia Pacific (Taipei) Region is ready to support your business. You can find a detailed list of the services available in this Region on the AWS Services by Region page. For news about AWS Region openings, check out the Regional news of the AWS News Blog.
Start building on the Asia Pacific (Taipei) Region now.


 Narayani Ambashta is an Analytics Specialist Solutions Architect at AWS, focusing on the automotive and manufacturing sector, where she guides strategic customers in developing modern data and AI strategies. With over 15 years of cross-industry experience, she specializes in big data architecture, real-time analytics, and AI/ML technologies, helping organizations implement modern data architectures. Her expertise spans across lakehouse, generative AI, and IoT platforms, enabling customers to drive digital transformation initiatives. When not architecting modern solutions, she enjoys staying active through sports and yoga.
 Raj Ramasubbu is a Senior Analytics Specialist Solutions Architect focused on big data and analytics and AI/ML with AWS. He helps customers architect and build highly scalable, performant, and secure cloud-based solutions on AWS. Raj provided technical expertise and leadership in building data engineering, big data analytics, business intelligence, and data science solutions for over 18 years prior to joining AWS. He helped customers in various industry verticals like healthcare, medical devices, life sciences, retail, asset management, car insurance, residential REIT, agriculture, title insurance, supply chain, document management, and real estate.
 Yadgiri Pottabhathini is a Senior Analytics Specialist Solutions Architect in the media and entertainment sector. He specializes in assisting enterprise customers with their data and analytics cloud transformation initiatives, while providing guidance on accelerating their Generative AI adoption through the development of data foundations and modern data strategies that leverage open-source frameworks and technologies.
 Junpei Ozono is a Sr. Go-to-market (GTM) Data & AI solutions architect at AWS in Japan. He drives technical market creation for data and AI solutions while collaborating with global teams to develop scalable GTM motions. He guides organizations in designing and implementing innovative data-driven architectures powered by AWS services, helping customers accelerate their cloud transformation journey through modern data and AI solutions. His expertise spans across modern data architectures including Data Mesh, Data Lakehouse, and Generative AI, enabling customers to build scalable and innovative solutions on AWS.