Tag Archives: cloud security

Aligning to AWS Foundational Security Best Practices With InsightCloudSec

Post Syndicated from Ryan Blanchard original https://blog.rapid7.com/2022/11/22/aligning-to-aws-foundational-security-best-practices-with-insightcloudsec/
Aligning to AWS Foundational Security Best Practices With InsightCloudSec

Written by Ryan Blanchard and James Alaniz

When an organization is moving their IT infrastructure to the cloud or expanding with net-new investment, one of the hardest tasks for the security team is to identify and establish the proper security policies and controls to keep their cloud environments secure and the applications and sensitive data they host safe.

This can be a challenge, particularly when teams lack the relevant experience and expertise to define such controls themselves, often looking to peers and the cloud service providers themselves for guidance. The good news for folks in this position is that the cloud providers have answered the call by providing curated sets of security controls, including recommended resource configurations and access policies to provide some clarity. In the case of AWS, this takes the form of the AWS Foundational Security Best Practices.

What are AWS Foundational Security Best Practices?

The AWS Foundational Security Best Practices standard is a set of controls intended as a framework for security teams to establish effective cloud security standards for their organization. This standard provides actionable and prescriptive guidance on how to improve and maintain your organization’s security posture, with controls spanning a wide variety of AWS services.

If you’re an organization that is just getting going in the cloud and has landed on AWS as your platform of choice, this standard is undoubtedly a really good place to start.

Enforcing AWS Foundational Security Best Practices can be a challenge

So, you’ve now been armed with a foundational guide to establishing a strong security posture for your cloud. Simple, right? Well, it’s important to be aware before you get going that actually implementing and operationalizing these best practices can be easier said than done. This is especially true if you’re working with a large, enterprise-scale environment.

One of the things that make it challenging to manage compliance with these best practices (or any compliance framework, for that matter) is the fact that the cloud is increasingly distributed, both from a physical perspective and in terms of adoption, access, and usage. This makes it hard to track and manage access permissions across your various business units, and also makes it difficult to understand how individual teams and users are doing in complying with organizational policies and standards.

Further complicating the matter is the reality that not all of these best practices are necessarily right for your business. There could be any number of reasons that your entire cloud environment, or even specific resources, workloads, or accounts, should be exempt from certain policies — or even subject to additional controls that aren’t captured in the AWS Foundational Security Best Practices, often for regulatory purposes.

This means you’ll want a security solution that has the ability to not just slice, dice, and report on compliance at the organization and account levels, but also lets you customize the policy sets based on what makes sense for you and your business needs. If not, you’re going to be at risk of constantly dealing with false positives and spending time working through which compliance issues need your teams’ attention.

Highlights from the AWS Foundational Security Best Practices Compliance Pack

There are hundreds of controls in the AWS Foundational Security Best Practices, and each of them have been included for good reason. In this interest of time this post won’t detail all of them, but will instead present a few highlights of controls to address issues that unfortunately pop up far too often.

KMS.3 — AWS KMS Keys should not be unintentionally deleted

AWS Key Management Service (AWS KMS) is a managed service that makes it easy for you to create and control the cryptographic keys used to encrypt and protect your data. It’s possible for keys to be inadvertently deleted. This can be problematic, because once keys are deleted they can never be recovered, and the data encrypted under that key is also permanently unrecoverable. When a KMS key is scheduled for deletion, a mandatory waiting period is enforced to allow time to correct an error or reverse the decision to delete. To help avoid unintentional deletion of KMS keys, the scheduled deletion can be canceled at any point during the waiting period and the KMS key will not be deleted.

Related InsightCloudSec Check: “Encryption Key with Pending Deletion”

[S3.1] — S3 Block Public Access setting should be enabled

As you’d expect, this check focuses on identifying S3 buckets that are available to the public internet. One of the first things you’ll want to be sure of is that you’re not leaving your sensitive data open to anyone with internet access. You might be surprised how often this happens.

Related InsightCloudSec Check: “Storage Container Exposed to the Public”

CloudFront.1 — CloudFront distributions should have origin access identity enabled

While you typically access content from CloudFront by requesting the specific object — or objects — you’re looking for, it is possible for someone to request the root URL instead. To avoid this, AWS allows you to configure CloudFront to return a “default root object” when a request for the root URL is made. This is critical, because failing to define a default root object passes requests to your origin server. If you are using an S3 bucket as your origin, the user would gain access to a complete list of the contents of your bucket.

Related InsightCloudSec Check: “Content Delivery Network Without Default Root Object”

Lambda.1 — Lambda function policies should prohibit public access

Like in the control highlighted earlier about publicly accessible S3 buckets, it’s also possible for Lambda to be configured in such a way that enables public users to access or invoke them. You’ll want to keep an eye out and make sure you’re not inadvertently giving people outside of your organization access and control of your functions.

Related InsightCloudSec Check: “Serverless Function Exposed to the Public”

CodeBuild.5 — CodeBuild project environments should not have privileged mode enabled

Docker containers prohibit access to any devices by default unless they have privileged mode enabled, which grants a build project’s Docker container access to all devices and the ability to manage objects such as images, containers, networks, and volumes. Unless the build project is used to build Docker images, to avoid unintended access or deletion of critical resources, this should never be used.

Related InsightCloudSec Check: “Build Project With Privileged Mode Enabled”

Continuously enforce AWS Foundational Security Best Practices with InsightCloudSec

InsightCloudSec allows security teams to establish and continuously measure compliance against organizational policies, whether they’re based on service provider best practices like those provided by AWS or tailored to specific business needs. This is accomplished through the use of compliance packs. A compliance pack within InsightCloudSec is a set of checks that can be used to continuously assess your cloud environments for compliance with a given regulatory framework or industry or provider best practices. The platform comes out of the box with 30+ compliance packs, including a dedicated pack for the AWS Foundational Security Best Practices.

InsightCloudSec continuously assesses your entire AWS environment for compliance with AWS’s recommendations, and detects non-compliant resources within minutes after they are created or an unapproved change is made. If you so choose, you can make use of the platform’s native, no-code automation to remediate the issue — either via deletion or by adjusting the configuration or permissions — without any human intervention.

If you’re interested in learning more about how InsightCloudSec helps continuously and automatically enforce cloud security standards, be sure to check out our bi-weekly demo series that goes live every other Wednesday at 1pm EST!
Better Cloud Security Shouldn’t Require Bigger Budgets

Post Syndicated from Aaron Wells original https://blog.rapid7.com/2022/11/17/better-cloud-security-shouldnt-require-bigger-budgets/

Stretching what you’re given

Better Cloud Security Shouldn’t Require Bigger Budgets

How can you do more when you’re constantly being given the same or less? When security budgets don’t match the pace of the cloud operations they’re tasked with securing, the only thing to do is become an expert in the stretch. It’s hard, and you might currently be under increasing stress to pull it all off.

While total overall budgets will indeed decrease, Gartner recently forecast that spending on cybersecurity and risk management would increase by 11.3% in 2023, driven in large part by a shift to cloud platforms. And what was a big factor in the increase in cloud adoption? You guessed it: the switch to remote or hybrid work models during the height of pandemic mitigation measures. These days you might have more to back up your argument for an increase in funding.

In the 2020 scramble to keep people safe by urging them to both stay home and stay employed, workforces quickly became virtual, more distributed, and incredibly reliant on cloud platforms to enable connectivity to each other. Businesses that might have dipped their toes in pre-pandemic are now taking the full cloud plunge post-pandemic.

The promise of the cloud is an interesting point to discuss. It can be cheaper to scale into the cloud, but depending on how it’s done and in what industry, it might actually require a bigger piece of the budget. But it can still be empowering and flexible. In other words, budgets will most likely keep increasing for cloud adoption. With all that said, if you’re still having trouble acquiring more budget for security, what should you do?

Finding the right fit

We’re not talking about a doomsday scenario where you’ll never see another increase in your budget. Cybersecurity and cloud security are top-of-mind topics for companies and nations around the world. However, solutions have evolved to address security organizations’ budgetary concerns. And there are reputable providers who have created offerings that can do more without asking more of your budget. This more-with-less scenario has the potential to satisfy across the board by helping you to:

  • Focus on use cases – What kind of cloud security do you need? Needlessly spending money on solutions you don’t need is tantamount to criminal behavior in the current global economic crisis. Make sure you know exactly what you need to protect, how far your perimeters extend, and the general types of available security (CSPM, CWPP, etc.). InsightCloudSec from Rapid7 is a unified platform that incorporates multiple use cases and types of cloud security.  
  • Extrapolate potential costs and prove security’s worth – Once you know what you need and the type(s) of solutions that can address it, it’s a good idea to partner with whomever controls your security budgets. Because it’s less about the costs or subscription fees you see today and more about extrapolating cost savings as cloud environments, data transfer, storage, and other aspects of that adoption grow. Then you’ll know how much or little you’ll need to engage in budget-stretching heroics.
  • Pinpoint under-one-umbrella solutions – Do you want to deal with one vendor or multiple? In the latter scenario, keep in mind the multiple support teams you’ll juggle as well as the different platforms on which those solutions will operate. There is no one-size-fits-all solution, but there are vendors that can provide a suite of broad-range capabilities so you have one point of contact and can better operationalize your cloud security.

About that whole “proving security’s worth” thing…

In this day and age, you really shouldn’t have to prove your organization’s worth. But you most likely feel that way every time you have to fight for a bigger piece of the budgetary pie. Sure, you can engage in stretching heroics, but should you have to engage in those heroics day in and day out, for years on end? Hopefully not now, when ransomware is still all the rage and nation-state-sponsored attacks are becoming more legitimate business in many parts of the world.  

Timing is everything, however, and now – at the end of the year – would be the time to pull off some of those heroics and make your case for more budget. This will enable your exploration into a solution that can do more for less. InsightCloudSec from Rapid7 is a cloud risk and compliance management platform that enables organizations to securely accelerate cloud adoption with continuous security and compliance throughout the entire software development lifecycle (SDLC).

It provides a comprehensive solution to manage and mitigate risk across even the most complex cloud environments. The platform detects risk signals in real-time and in complete context, allowing your teams to focus on the issues that present the most risk to your business based on potential impact and likelihood of exploitation.

And speaking of making things easier

Whatever your ultimate cloud security needs are, you can now learn more about tactics to help you make your case for more – or any – cloud security at your company. Plus, get a handy checklist to use when looking into a potential solution. Get started now with the 2022 edition of The Complete Cloud Security Buyer’s Guide from Rapid7. You can also read the previous entry in this blog series here.

Rapid7 and HashiCorp Partner to Secure Terraform-based Cloud Infrastructure Deployments

Post Syndicated from Clint Merrill original https://blog.rapid7.com/2022/11/17/rapid7-and-hashicorp-partner-to-secure-terraform-based-cloud-infrastructure-deployments/

Rapid7 and HashiCorp Partner to Secure Terraform-based Cloud Infrastructure Deployments

Welcome to the latest installment in our cloud security “shift-left” blog series. In our last post, we covered the importance of integrating cloud infrastructure security assessments into DevOps tools and enabling Infrastructure as Code (IaC) developers. This time, we’re focusing on Rapid7’s recent partnership with Hashicorp, ongoing support for scanning Terraform plans with our IaC security feature, and the recently released integration with Terraform Cloud & Enterprise run tasks.

HashiCorp Terraform and InsightCloudSec are a powerful combination

Rapid7 and HashiCorp Partner to Secure Terraform-based Cloud Infrastructure Deployments

There are countless reasons to adopt cloud infrastructure: hosting applications, compute workloads, data storage, virtual networking, governing identity and access control, and many other use-cases. We are spoiled for choice with the vast array of cloud resources and services designed to perform specific tasks, but each one requires specialized knowledge to configure it securely and interact with other resources. Additionally, resilient cloud applications typically leverage best-in-class features from multiple cloud service providers (CSPs) who compete with innovation, unique features and cost optimization. The more distributed your cloud resources are across providers, the more powerful it is to define them via IaC with a tool that can deploy to any provider.

HashiCorp Terraform is a widely-used open-source IaC tool, especially for supporting multi-cloud deployments. InsightCloudSec has the ability to scan Terraform plans destined for accounts in AWS, Azure or GCP. Rapid7 supports the key resource types for each of the three major cloud providers, and we are constantly expanding our coverage based on usage trends or as needed by our customers.

A major benefit of using InsightCloudSec for IaC security and compliance scans is that you can use the same Insight Compliance Pack for assessing runtime environments and IaC, rather than correlating policy definitions across different tools. This reduces the overhead of maintaining multiple policies and the associated rules across different tools and languages which can easily drift apart. We call this “One Policy”.

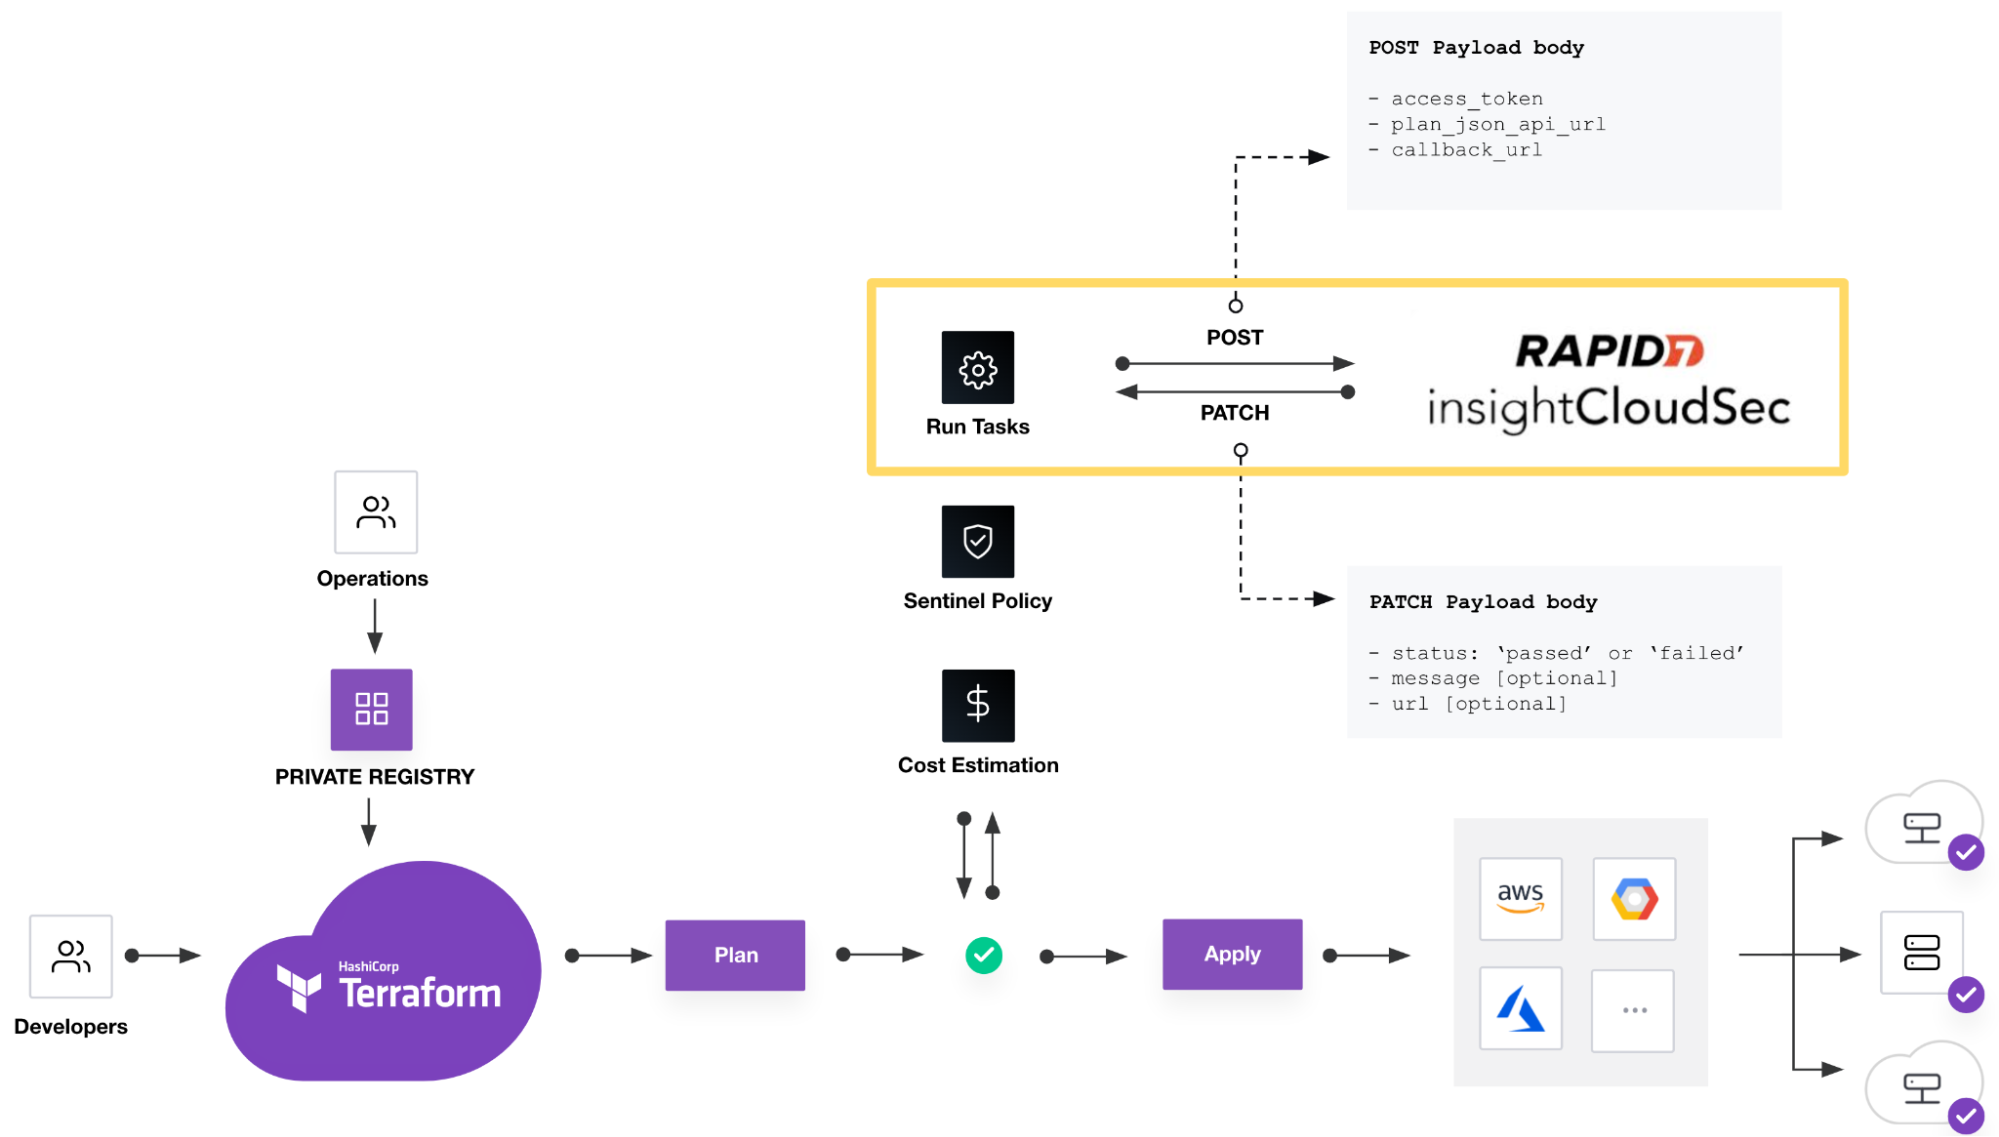
Terraform allows users to develop immutable cloud resource definitions as code in a common language for deployment to multiple cloud providers. When paired with InsightCloudSec, resource definitions can be assessed with a single set of security policies applied to both development and runtime environments—creating an optimized experience that delivers efficiency and convenience. To further power this union, Rapid7 has partnered with HashiCorp to develop a formal integration between Terraform Cloud and InsightCloudSec (ICS).

New integrations with HashiCorp Terraform Cloud and Terraform Enterprise run tasks

IaC developers create Terraform configurations using HashiCorp configuration language (HCL) and commit them to a source code repository such as Git. The Terraform configuration and the current infrastructure state are evaluated to generate a deployment plan—a preview of changes that will be made in the destination cloud account(s). By linking HCL configurations to collections of resources defined as workspaces in Terraform Cloud, deployment plans are generated and await approval to apply them. At this point, run tasks are used to invoke analysis of the plan, including security and compliance checks in external tools to inform or gate the approval step. This process can be managed through workflows on one of many supported CI/CD platforms; however, HashiCorp developed Terraform Cloud and Enterprise to govern, optimize and secure the process.

DevOps teams using Terraform Cloud to govern cloud infrastructure deployments can securely and reliably trigger a security and compliance assessment of a Terraform plan in ICS using a run task. We’ve worked with the team at HashiCorp to streamline the process of linking a run task to an IaC Configuration in ICS which defines the security policy (Insight Compliance Pack) that will be used to assess the Terraform plan.

Rapid7 and HashiCorp Partner to Secure Terraform-based Cloud Infrastructure Deployments

This investment is the latest step in our strategy at Rapid7 to directly support DevOps teams to apply IaC security using the tool of their choice. Terraform Cloud was at the top of our list for a formal integration given its prevalent use in the cloud infrastructure and application development community.

Ready to get started?

Configuring the new integrations with Terraform is a straightforward process, but let’s walk through it at a high level. Assuming you’ve configured your Terraform Cloud or Enterprise environment with workspaces to generate plans, we’ll show you how to link a Run Task to an IaC Configuration in ICS. Detailed instructions are available in the ICS Product Documentation.

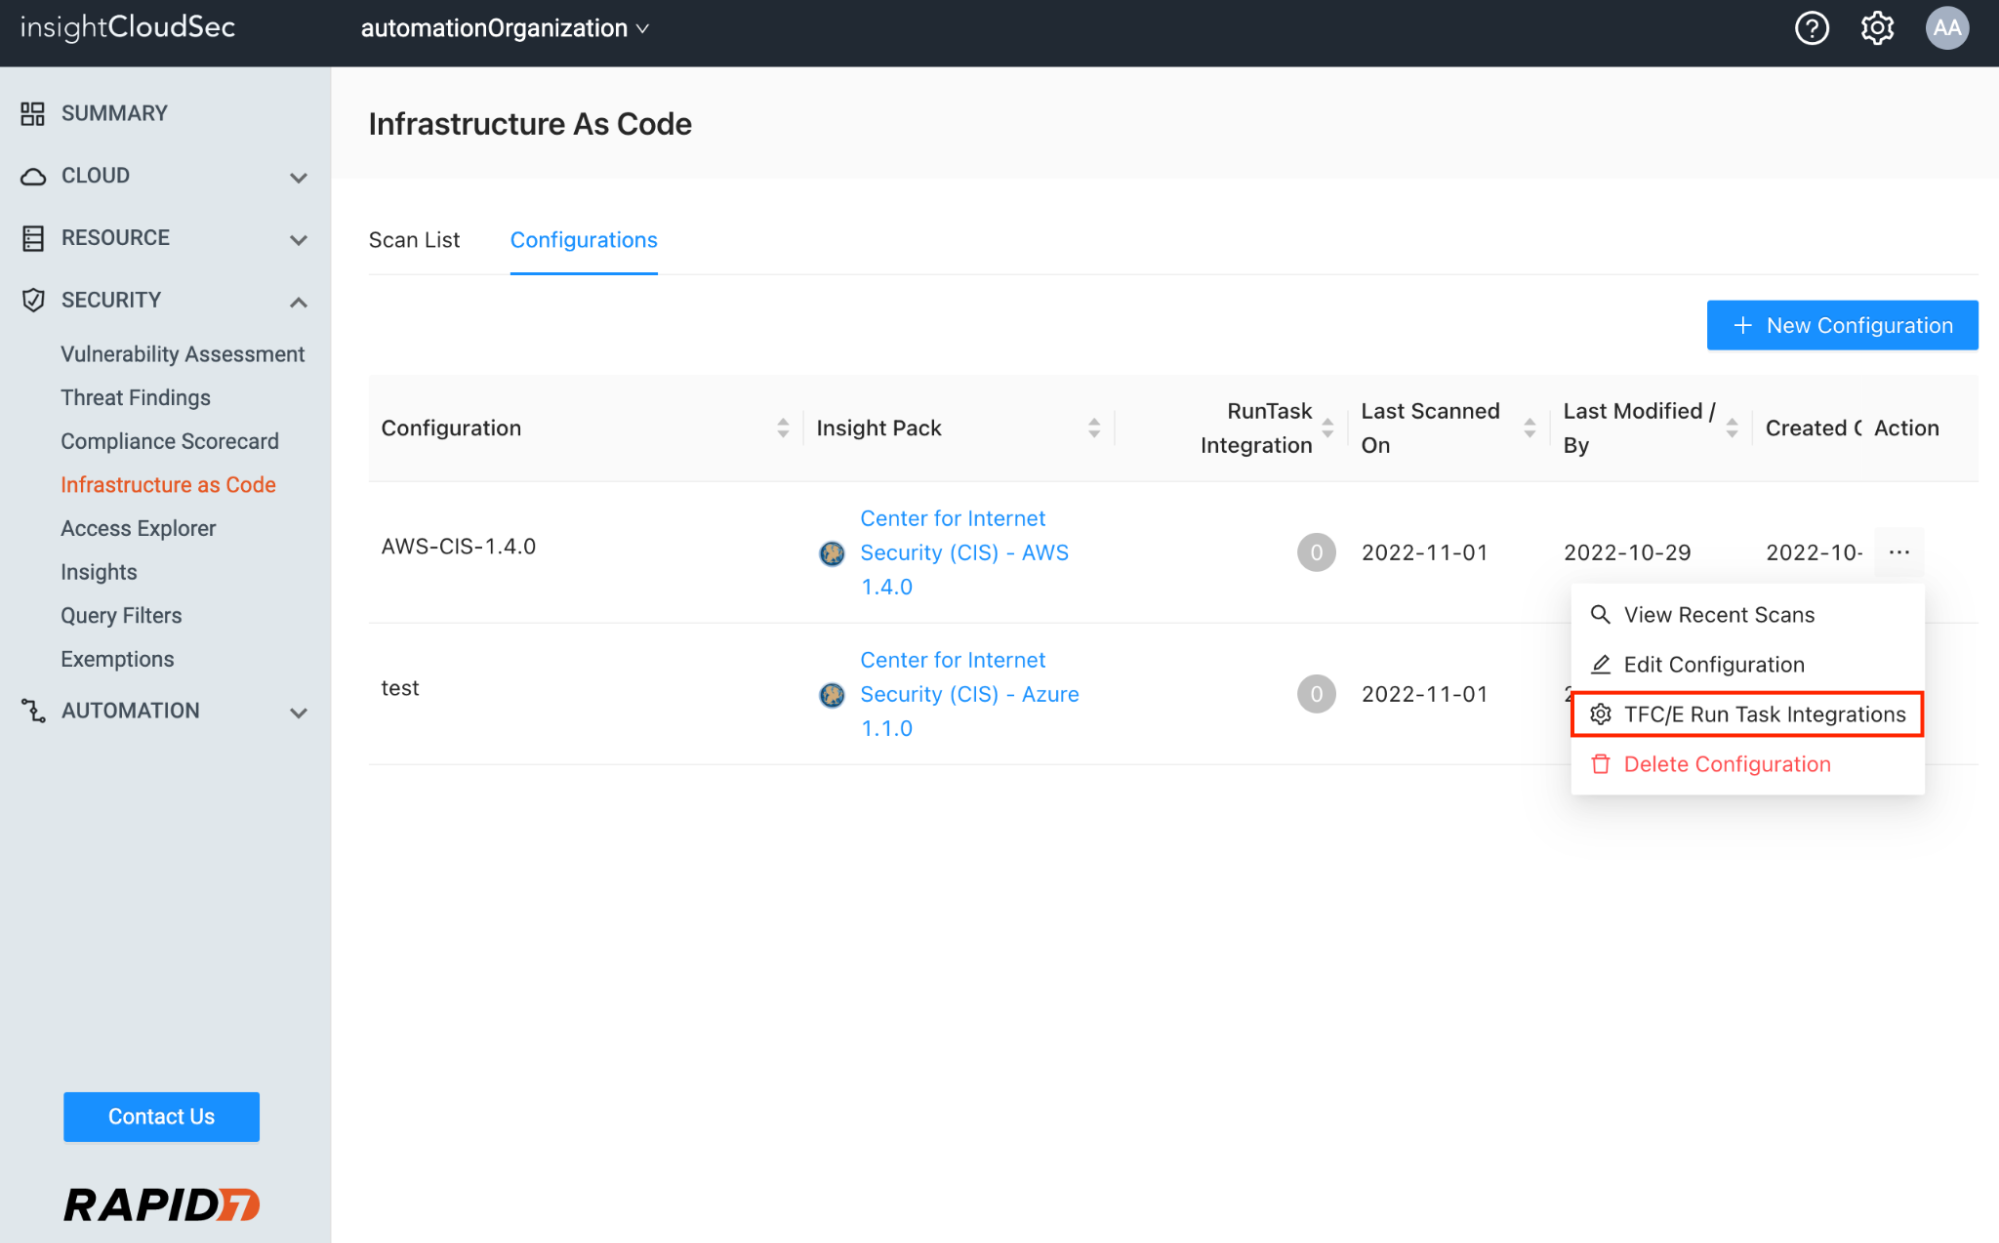
Visit the Infrastructure as Code landing page and select the Configurations tab at the top. Any existing Configuration defined to support scanning Terraform plans can be linked to a run task.  Click the Action menu and select the “TFC/E Run Task Integrations” option.

Rapid7 and HashiCorp Partner to Secure Terraform-based Cloud Infrastructure Deployments

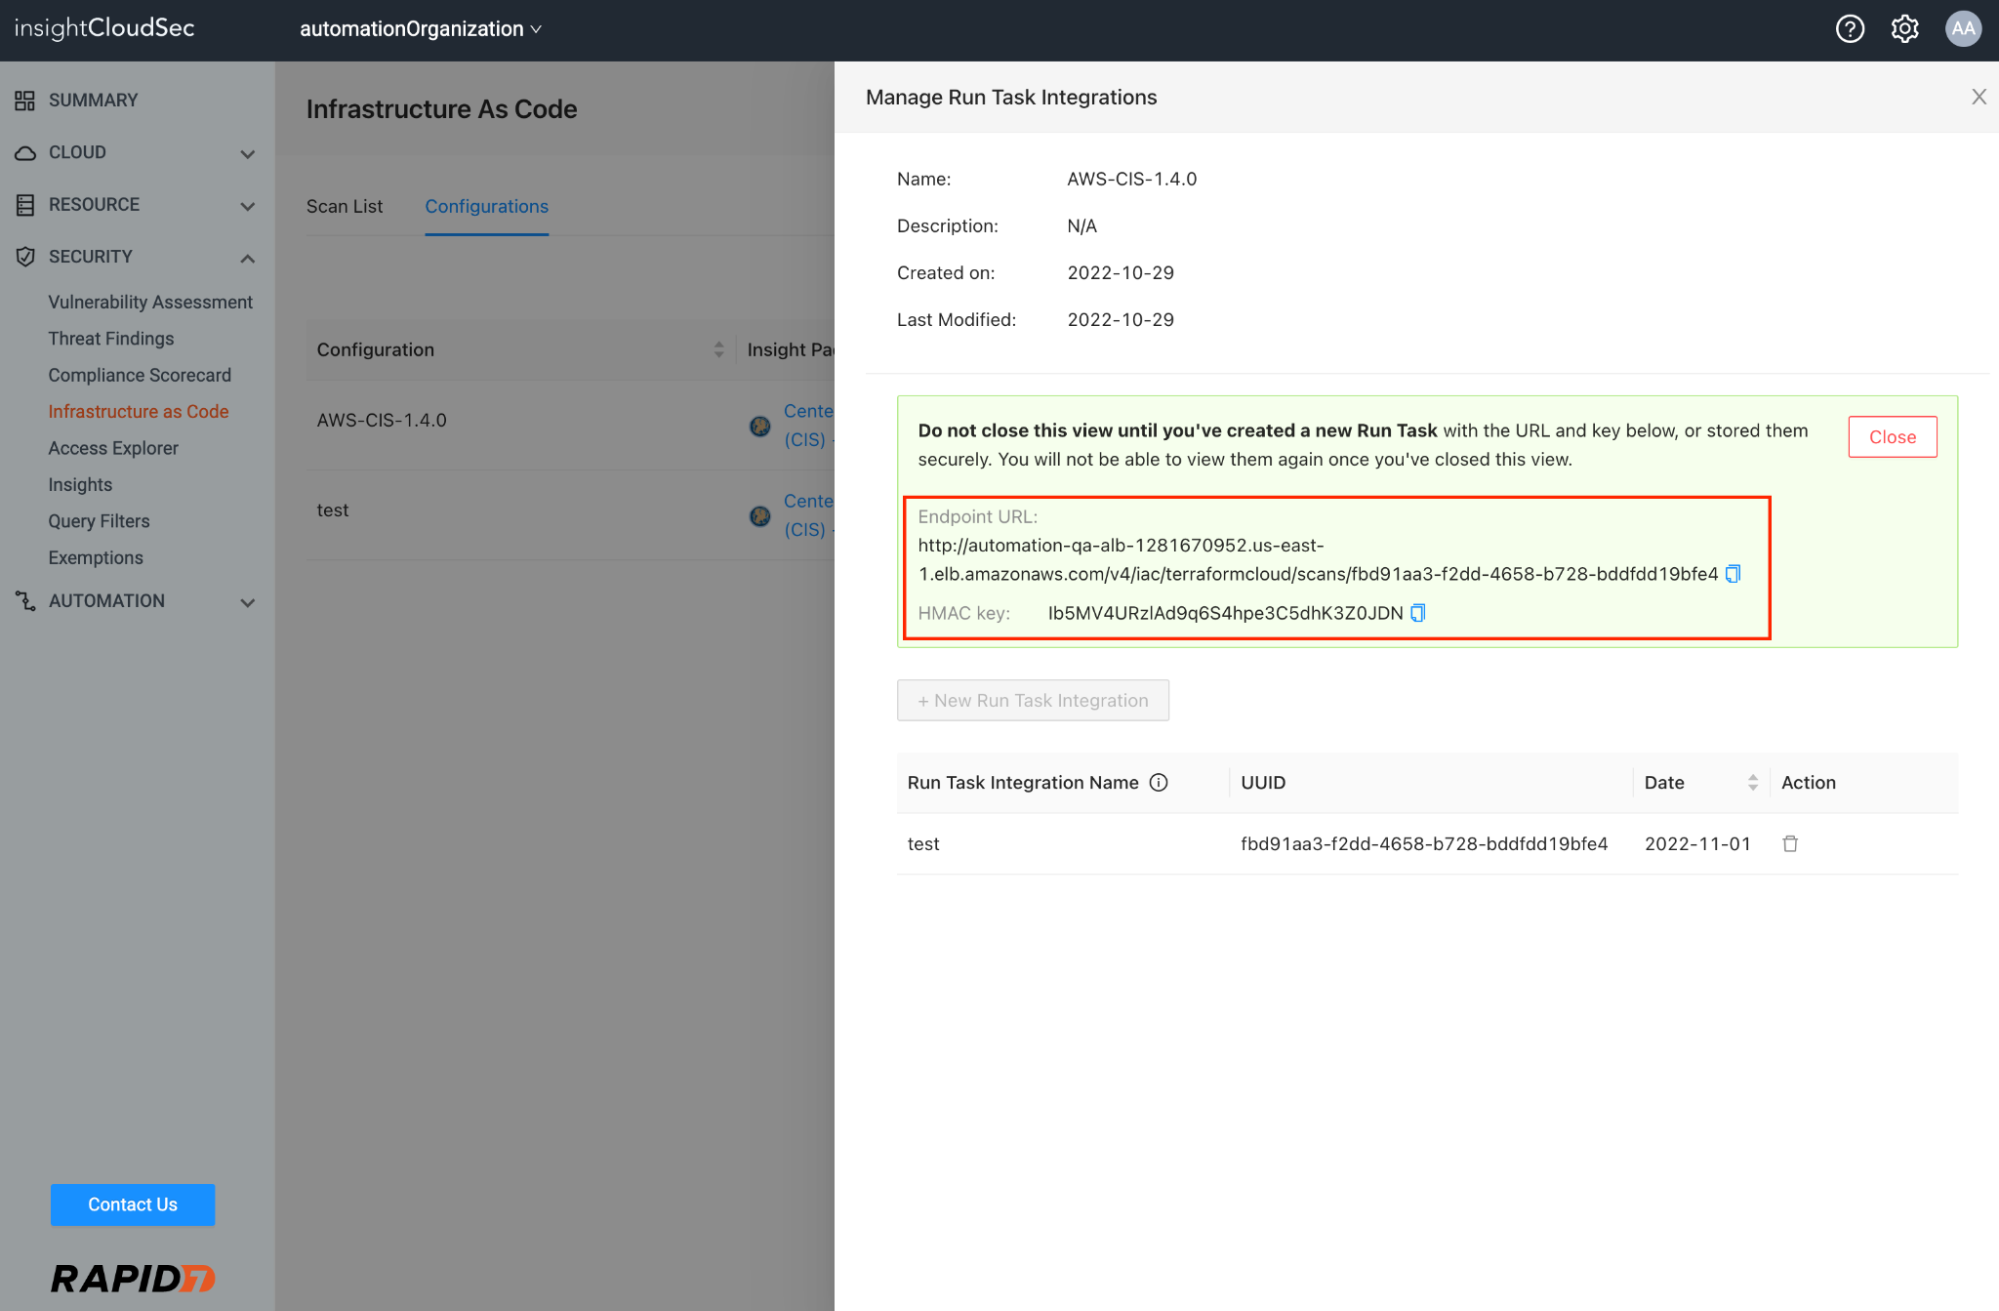
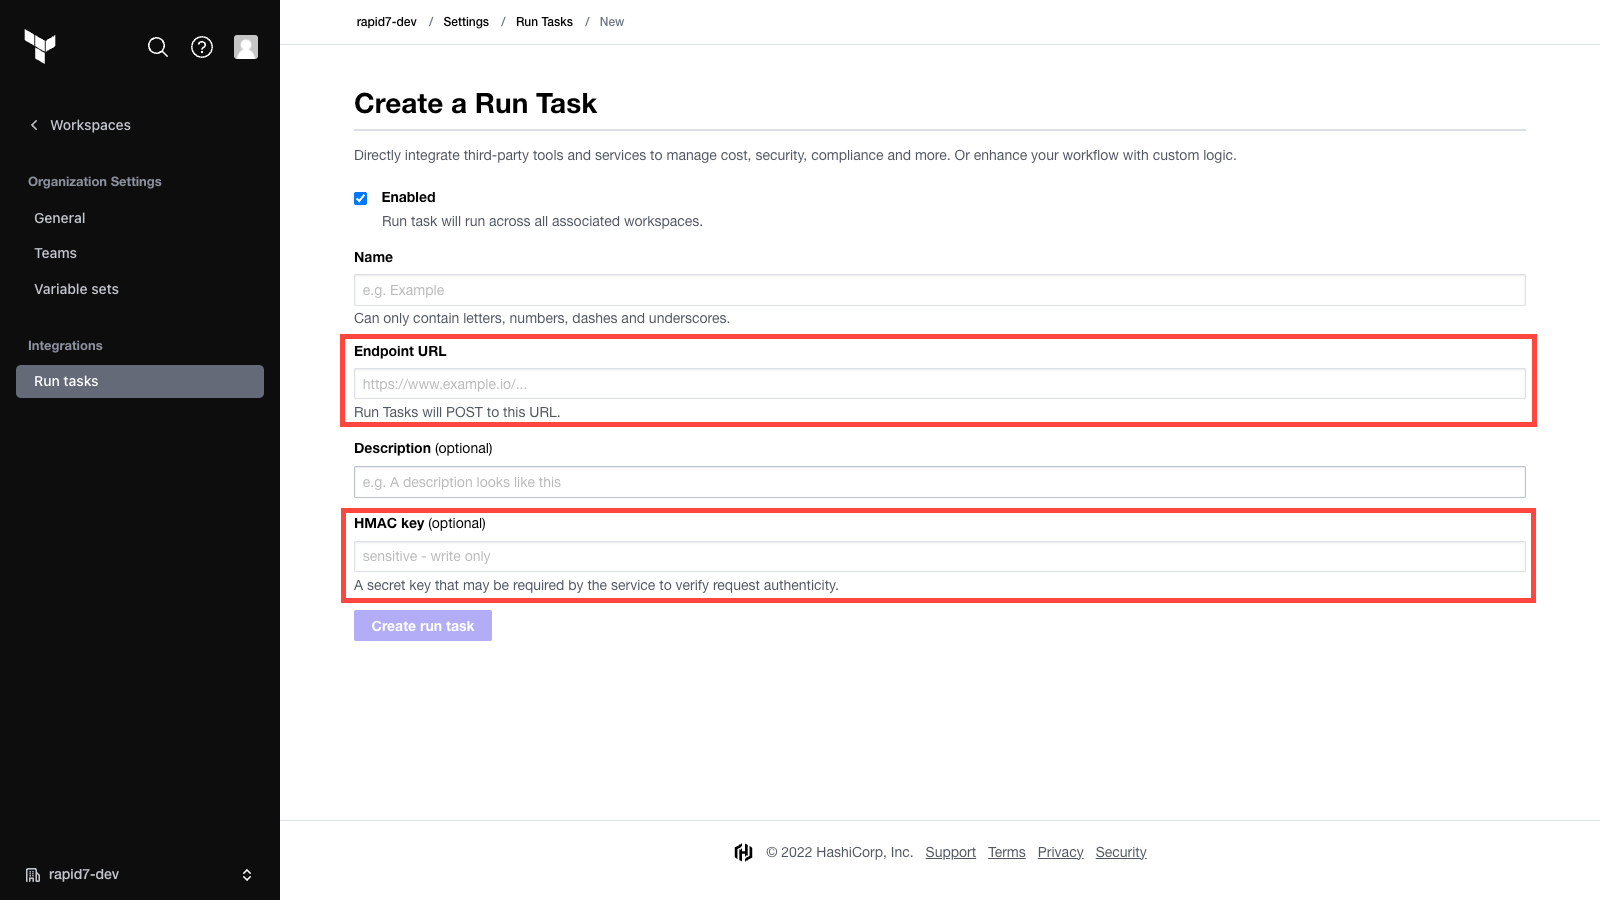
From there, you’ll generate an unique Endpoint URL and HMAC key used during the creation of the run task in Terraform Cloud to securely bind the two systems.

Rapid7 and HashiCorp Partner to Secure Terraform-based Cloud Infrastructure Deployments

Next, switch to the Terraform Cloud / Enterprise organization settings interface and create a run task. Copy/paste the Endpoint URL and HMAC key provided to you in ICS.

Rapid7 and HashiCorp Partner to Secure Terraform-based Cloud Infrastructure Deployments

After the run task is successfully created, you will need to associate it with a workspace before generating a plan and triggering it to test the end-to-end process.

During the run task execution, you’ll notice active communication between the two systems monitoring the state of the scan job in ICS and reporting back a final state as Passed, Failed, or Error (indicating the scan job didn’t successfully complete).

We’ve made this integration process simple and accessible to DevOps teams via ICS and Terraform Cloud without any custom API integration required. You can ensure IaC security and compliance scans in ICS are routinely applied to the approval step before Terraform plans are applied to a destination cloud environment.

Our DevOps-focused cloud security investment continues

Rapid7’s InsightCloudSec is proud to partner with HashiCorp to help fulfill the joint mission of making cloud infrastructure and application development and maintenance low cost, code-driven, repeatable, scalable and secure.

For more information , please visit HashiCorp’s partnership page.

Our next blog in the “shift-left” series will include an announcement and overview of a significant upgrade we’re making to our IaC scanning engine and the underlying technology we use to identify issues, pinpoint the location of the problem in code, and provide ‘Actionable Results’ to assist developers with remediation.

Cloud Security: Buyer Be Critical

Post Syndicated from Aaron Wells original https://blog.rapid7.com/2022/11/10/cloud-security-buyer-be-critical/

Tailoring solutions to challenges

Cloud Security: Buyer Be Critical

It takes a toolbox with different, well, tools to secure an ever-expanding operational perimeter in the cloud. Think about what’s under the general daily purview of cloud security teams: preventing misconfigurations, taming threats and vulnerabilities, and so much more. Now, apply that to different high-risk industries around the globe that must build and tailor cloud security solutions to their unique challenges. For instance:

  • Financial Services: It can be difficult trying to leverage the benefits of digital transformation while attempting to modernize decades of tradition in an old-school industry. Mobile banking/financial services, for instance, has been the one of the largest industry shifts over the past decade and has accelerated cloud adoption in the sector. Thus, security must keep pace with the service’s rapid growth. The desire to operationalize on-premises and cloud practices is typically strong in this industry, but must also take into account client trust in a financial-services partner to protect that client’s bottom line.    
  • Healthcare: With the growing normalization of telehealth services across the spectrum of medical providers, it’s more critical than ever to secure patient health information (PHI) while adhering to regulatory standards like HIPAA. The need for speed and innovation in medicine is critical, so scaling communication and technology operations into the cloud can be incredibly beneficial. However, providers are also continually challenged with securing PHI within new technologies at speed and scale without slowing innovation.    
  • Automotive: With the modernization of engines, software, and connectivity, the need for passenger safety is more important than ever. As more automobile controls are conveniently accessible through cloud-based controls, cyberattacks have correspondingly increased. Ensuring security checks are implemented in the production and design of a new vehicle while also pushing software updates throughout the ownership lifecycle of that vehicle is critical to manufacturer integrity and passenger safety.

Expansive perimeters

Within and throughout these different use cases and industries are specific budgetary constraints that have prompted organizations to scale cloud operations at unprecedented speeds – no doubt accelerated in large part by the pandemic as it was in its early stages a couple of years ago. Do companies want to go back to not saving money? Certainly not. That means attackers are as ready as they’ll ever be to try and break expanding cloud perimeters.

With your company’s reputation at risk, it’s more critical than ever that security keeps pace with those expanding perimeters, particularly at a time of global financial crisis for many companies as they emerge from the pandemic. Whether a company is looking for a partner to alleviate financial strain in a potential merger situation or seeking an outright buyer, the security of the merged or acquired company’s cloud-hosted operations – particularly vulnerable to attackers during a time of change – is paramount.

High-profile recent examples of the above include Discovery, Inc.’s purchase of WarnerMedia, Elon Musk’s acquisition of Twitter, and Microsoft’s acquisition of Activision Blizzard. These are tectonic shifts for all companies involved, of a sort that can leave cloud security extremely vulnerable at certain points in the process. And the higher-profile the company, the more attractive it can be to an attacker.

Evaluating solutions at speed and scale

So, you’re seeking a strongly effective solution. But, the cloud security vendor space can be confusing. One provider defines cloud security a certain way and another defines it a separate way, and their offerings differ accordingly. Between CASB, SaaS Security, CSPM, and CWPP solutions, there’s a lot to learn. Are any of these right for your cloud operations? There is no one-size-fits-all solution, but you may find a suite of tools that can best work for your specific use case(s).

There are any number of cloud security guides, whitepapers, research, and more that can help you evaluate solutions available from reputable providers. The latest edition of The Complete Cloud Security Buyer’s Guide is a timely and discerning dive into different types of cloud security and the use cases to which they align. Get help with the process of evaluating vendors, while taking into account the need for speed in deploying effective security that protects ever-expanding operational perimeters in the cloud.

Explore how to make the best case for more – or any – cloud security at your company, plus get a handy checklist to use when looking into a potential solution. Get started now with the 2022 edition of The Complete Cloud Security Buyer’s Guide from Rapid7.

Common questions when evolving your VM program

Post Syndicated from Rapid7 original https://blog.rapid7.com/2022/11/02/common-questions-when-evolving-your-vm-program/

Common questions when evolving your VM program

Authored by Natalie Hurd

Perhaps your organization is in the beginning stages of planning a digital transformation, and it’s time to start considering how the security team will adapt. Or maybe your digital transformation is well underway, and the security team is struggling to keep up with the pace of change. Either way, you’ve likely realized that the approach you’ve used with traditional infrastructure will need to evolve as you think about managing risk in your modern ecosystem. After all, a cloud instance running Kubernetes clusters to support application development is quite different from an on-premise Exchange server!

A recent webinar led by two of Rapid7’s leaders, Peter Scott (VP, Product Marketing) and Cindy Stanton (SVP, Product and Customer Marketing), explored the specific challenges of managing the evolution of risk across traditional and cloud environments. The challenges may be plentiful, but the strategies for success are just as numerous!

Over the course of several years, Rapid7 has helped many customers evolve their security programs in order to keep pace with the evolution of technology, and Peter and Cindy have noticed some themes of what tends to make these organizations successful. They advise working with your team & other stakeholders to find answers to the following questions:

  • What sorts of resources does your organization run in the cloud, and who owns them?
  • What does “good” look like when securing your cloud assets, and how will you measure success?
  • Which standards and frameworks is your company subject to, compliance or otherwise?

Gathering answers to these questions as early as possible will not only aid in the efficacy of your security program, it will also help to establish strong relationships & understanding amongst key stakeholders.

Establishing Ownership


Common questions when evolving your VM program

Proactively identifying teams and individuals that own the assets in your environment will go a long way towards ensuring speed of resolution when risk is present. Peter strongly suggests working with your organization’s Product or Project Development teams to figure out who owns what and get it documented. This way, when you see a misconfiguration, vulnerability or threat that needs to be dealt with, you know exactly who to talk to to get it resolved, saving important time.

The owners that you identify will not only have a hand to play in fixing problems, they can help make the necessary changes to “shift left” and prevent problems in the first place. The sooner you can identify these stakeholders and build relationships with them, the more successful you’ll be in the long run.

Defining “Good” and Tracking Achievement


Common questions when evolving your VM program

Since we’ve established that securing traditional environments is not the same as securing modern environments, we can also agree that the definition of success may not be the same either! After you’ve established ownership, Cindy notes that it’s also important to define what “good” looks like, and how you plan to measure & report on it. Once you’ve created a definition of “good” within your immediate team, it’s also important to socialize that with stakeholders across your organization and track progress towards achieving that state. Tracking & sharing progress is valuable whether your organization meets, exceeds or falls short of your goals; celebrating the wins is just as important as seeking to understand the losses!

Aligning to Standards and Frameworks


Common questions when evolving your VM program

Every industry comes with its own set of compliance and regulatory standards that must be adhered to, and it’s important to understand how security fits in. Your team can use these frameworks as a North Star of sorts when considering how to secure your environment, and the cloud aspects of your environment are no exception. Ben Austin, the moderator of the webinar, provides some perspective on the utility of compliance as a method for demonstrating progress in risk reduction. If your assets are more compliant today than they were 3 months ago, that’s a win for every stakeholder involved. If assets are getting less compliant, then you can work with your already-identified asset owners to make a plan to turn the ship around, and contextualize the importance of remaining compliant with them.

Check out our two previous blogs in the series to learn more about Addressing the Evolving Attack Surface and Adapting your VM Program to Regain Control, and watch the full webinar replay any time!

Adapting existing VM programs to regain control

Post Syndicated from Ryan Blanchard original https://blog.rapid7.com/2022/10/24/adapting-existing-vm-programs-to-regain-control/

Adapting existing VM programs to regain control

Stop me if you’ve heard this before. The scale, speed and complexity of cloud environments — particularly when you introduce containers and microservices — has made the lives of security professionals immensely harder. While it may seem trite, the reason we keep hearing this refrain is because, unfortunately, it’s true. In case you missed it, we discussed how cloud adoption creates a rapidly expanding attack surface in our last post.

One could argue that no subgroup of security professionals is feeling this pain more than the VM team. From elevated expectations, processes, and tooling to pressured budgets, the scale and complexity has made identifying and addressing vulnerabilities in cloud applications and the infrastructure that supports them a seemingly impossible task. During a recent webinar, Rapid7’s Cindy Stanton (SVP, Product and Customer Marketing) and Peter Scott (VP, Product Marketing) dove into this very subject.

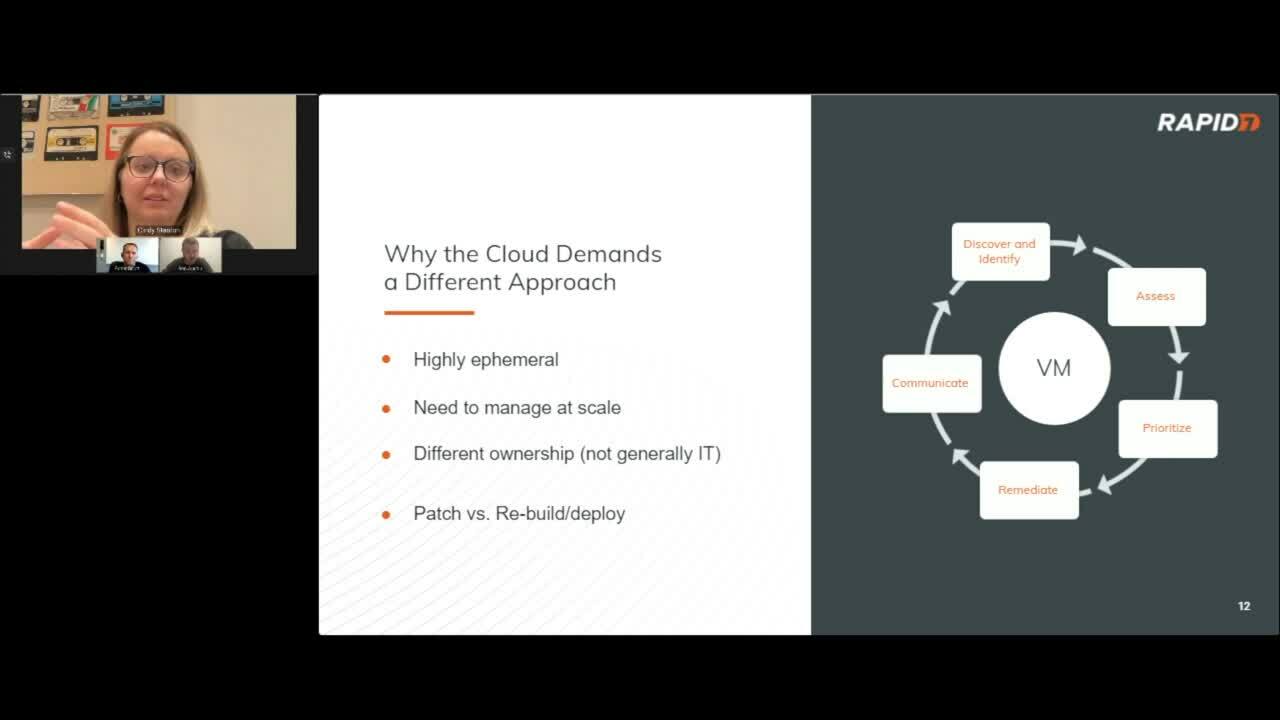
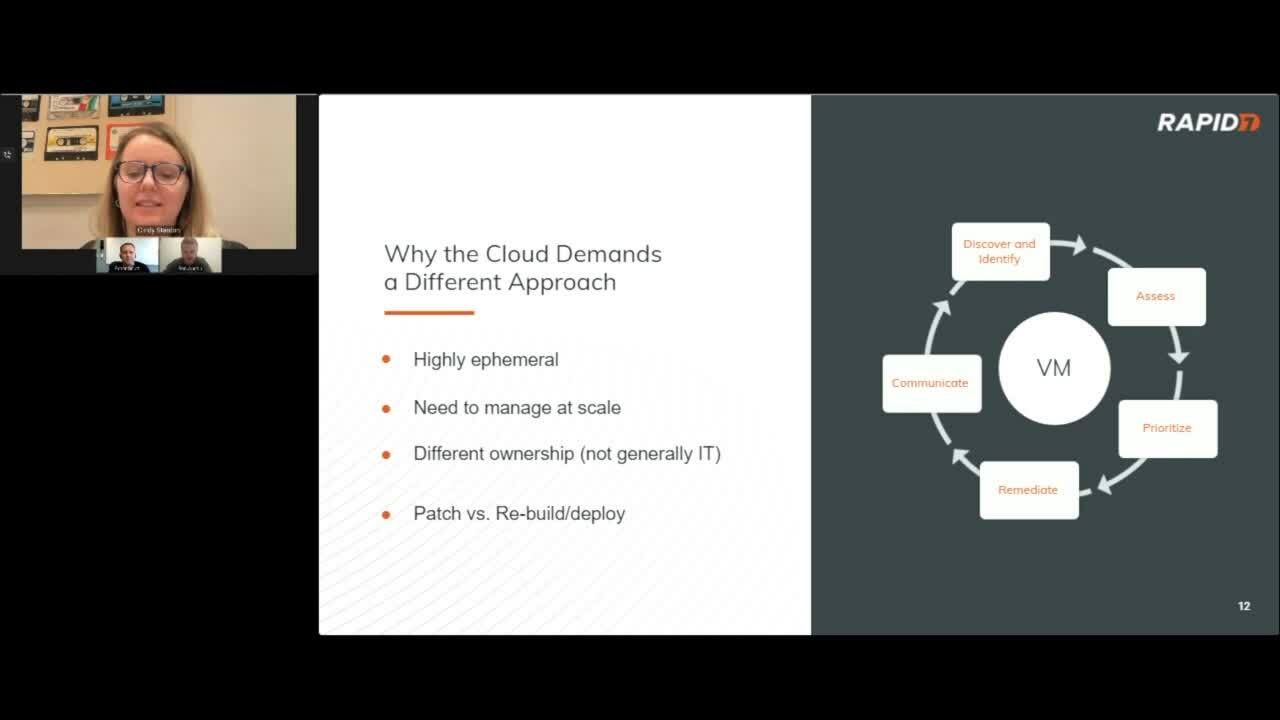
Cindy starts off this section by unpacking why modern cloud environments require a fundamentally different approach to implementing and executing a vulnerability management program. The highly ephemeral nature of cloud resources with upwards of 20% of your infrastructure being spun down and replaced on a daily basis makes maintaining continuous and real-time visibility non-negotiable. Teams are also being tasked with managing exponentially larger environments, often consisting of 10s of thousands of instances at any given moment.


Adapting existing VM programs to regain control

To make matters worse, it doesn’t stop at the technical hurdles. Cindy breaks down how ownership of resources and responsibilities related to addressing vulnerabilities once they’re identified has shifted. With traditional approaches it was typical to have a centralized group (typically IT) that owned and was ultimately responsible for the integrity of all resources. Today, the self-serve and democratized nature of cloud environments has created a dynamic in which it can be extremely difficult to track and identify who owns what resource or workload and who is ultimately responsible to remediate an issue when one arises.


Adapting existing VM programs to regain control

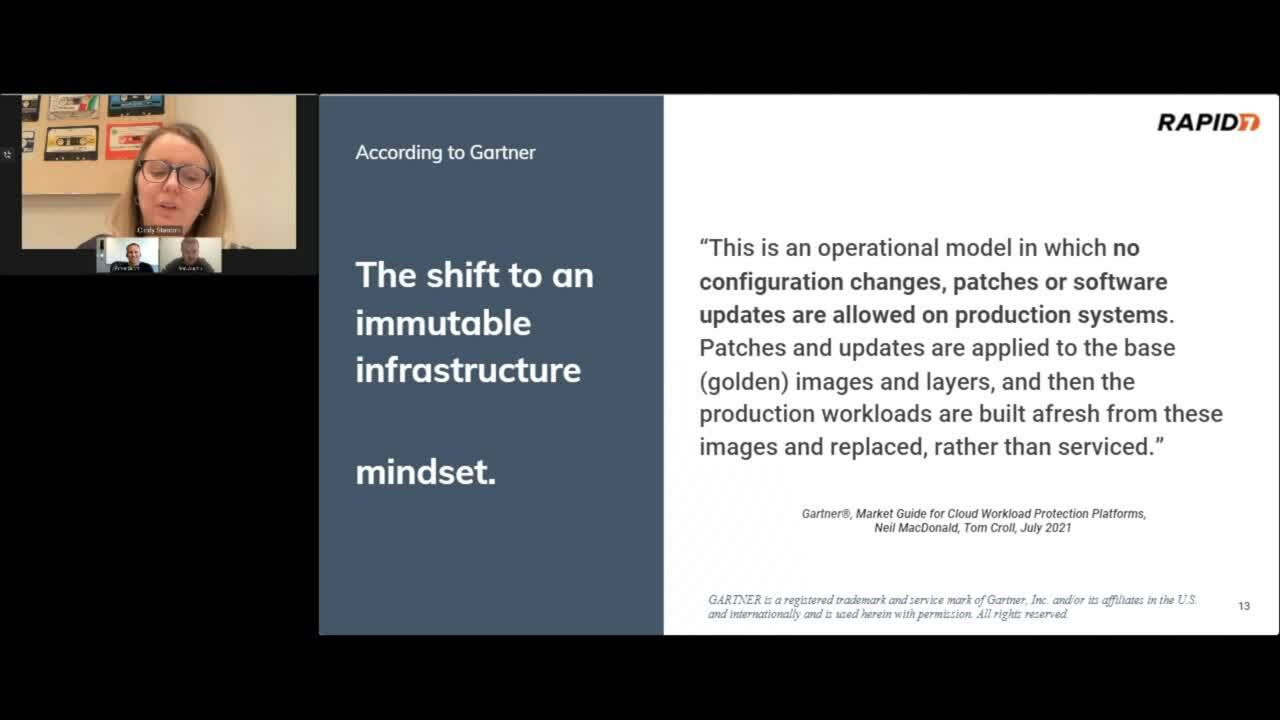
Cindy goes on to outline how drastically remediation processes need to shift when dealing with immutable infrastructure (i.e. containers) and how that also requires a shift in mindset. Instead of playing a game of whack-a-mole in production workloads trying to address vulnerabilities, the use of containers introduces a fundamentally new approach centered around making patches and updates to base images — often referred to as golden images — and then building new workloads from scratch based off of the hardened image rather than updating and retaining the existing workload. As Cindy so eloquently puts it, “the ‘what’ I have to do is relatively unchanged, but the ‘how’ really has to shift to adjust to this different environment.”


Adapting existing VM programs to regain control

Peter follows up Cindy’s assessment of how cloud impacts and forces a fundamentally different approach to VM programs by providing some recommendations and best practices to adapt your program to this new paradigm as well as how to operationalize cloud vulnerability management across your organization. We’ll cover these best practices in our next blog in this series, including shifting your VM program left to catch vulnerabilities earlier on in the development process. We will also discuss enforcing proper tagging strategies and the use of automation to eliminate repetitive tasks and accelerate remediation times. If you’re interested in learning more about Rapid7’s InsightCloudSec solution be sure to check out our bi-weekly demo, which goes live every other Wednesday at 1pm EST. Of course, you can always watch the complete replay of this webinar anytime as well!

Emerging best practices for securing cloud-native environments

Post Syndicated from Rapid7 original https://blog.rapid7.com/2022/10/18/emerging-best-practices-for-securing-cloud-native-environments/

Emerging best practices for securing cloud-native environments

Globally, IT experts recognise security as the most significant barrier to cloud adoption, in part because  many of the ways of securing traditional IT environments are not always applicable to cloud-native infrastructure. As a result, security teams may find themselves behind the curve and struggling to keep up with the ambitious digital transformation programs set by their senior leadership teams.

As technology evolves and threats change rapidly, organizations that stay abreast of the latest developments, trends, and industry standards tend to have fewer security risks than those that don’t. Failure to do so can lead to data breaches, compliance violations and increased costs. From creating a security culture to implementing innovative solutions, it’s clear a new approach to security is required; one that is more automated and based on best practices that consider the following:

Speed vs security

Finding the right balance between security and speed can be difficult, especially when trying to keep pace with your organization’s cloud migration and digital transformation strategy. Securing your continuous integration and delivery (CI/CD) pipeline can be challenging if visibility, governance and compliance lack across your IT environment.

Ensuring errors and missteps are detected and minimised requires a consistent set of processes, people, and tools. By putting challenges into logical groups, you can address each one more effectively.

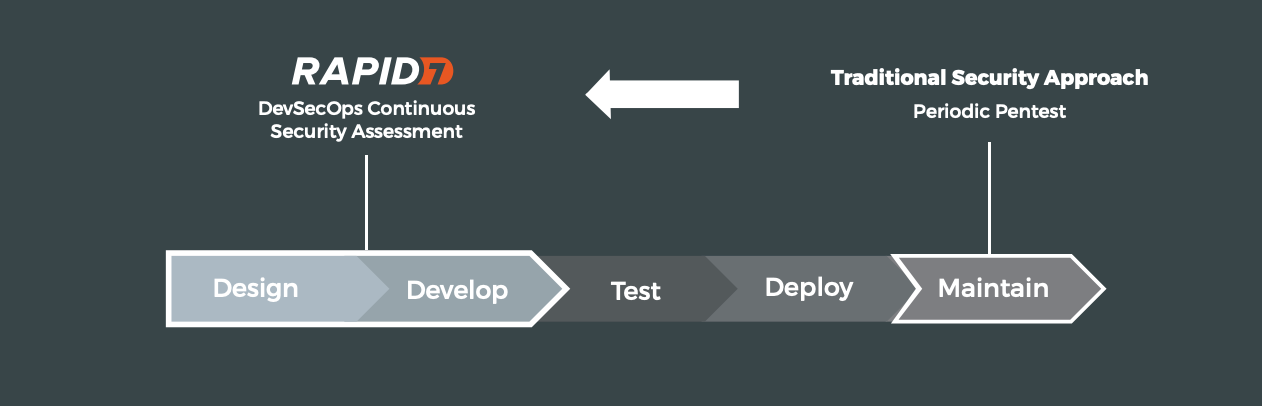
For example, the first stage of the CI/CD pipeline is vulnerable to human error. Adopting the DevSecOps model adds security to the DevOps working processes as a continuous activity, allowing security policies to be defined and enforced at every pipeline stage — including development and testing environments. Although, moving away from traditional processes requires strong foundations to transform and change.

Operationalising cyber security

As the number of workloads in the cloud increases, security challenges can sometimes fall between the gaps and outside of traditional processes, increasing additional risk from a technical and operational perspective. When everyone understands cybersecurity processes, their importance and why it’s necessary, they’ll take action. Holding people and business units accountable for their efforts lets you measure your cyber security programs’ effectiveness to discover any necessary improvements. This will result in better decision-making and measurable risk reduction; not to mention greater understanding and awareness of security across your organization.

Begin by understanding where and how security gaps are being created. Once you’ve identified these gaps, prioritise them based on business impact and the likelihood of occurrence. Ask your peers; in the event of a breach, what data would you be most concerned about if hackers applied ransomware to it? With this information in hand, it becomes easier to identify the appropriate controls and solutions to help identify your organization’s cyber maturity.

Knowledge sharing

Encouraging knowledge sharing is a great way to help address the skills gap. The more we share our experiences, the easier it is to improve processes and procedures to reduce the risk of mistakes reoccurring. But how do you make sure you get it right?

Join Alex Noble, cloud security lead and Jason Hart, chief technology officer EMEA, for our Lunch and Learn Series: Stay ahead of the curve. During these exclusive, interactive virtual sessions, we will explore emerging best practices driven by new technologies and evolving business models. Don’t miss your chance to connect with local peers and team members over a complimentary virtual lunch.

Join the conversation and save your seat.

Cloud IAM Done Right: How LPA Helps Significantly Reduce Cloud Risk

Post Syndicated from Ryan Blanchard original https://blog.rapid7.com/2022/10/14/cloud-iam-done-right-how-lpa-reduces-cloud-risk/

Cloud IAM Done Right: How LPA Helps Significantly Reduce Cloud Risk

Today almost all cloud users, roles, and identities are overly permissive. This leads to repeated headlines and forensic reports of attackers leveraging weak identity postures to gain a foothold, and then moving laterally within an organization’s modern cloud environment.

This has become a prevalent theme in securing the cloud, where identity and access management (IAM) plays a much larger role in governing access than in traditional infrastructure. However, the cloud was built for innovation and speed, with little consideration as to whether the access that has been granted is appropriate. The end result is an ever-growing interconnected attack surface that desperately needs to be tailored down.

To govern and minimize IAM risk in the cloud, organizations need to adopt the principle of least privilege access (LPA). Rapid7 is pleased to announce the release of LPA Policy Remediation as part of its InsightCloudSec product line. If you’re not familiar, InsightCloudSec is a fully-integrated cloud-native security platform (CNSP) that enables organizations to drive cloud security forward through continuous security and compliance. The platform provides real-time visibility into everything running across your cloud environment(s), detecting and prioritizing risk signals (including those associated with IAM policies), privileges, and entitlements, and provides native automation to return resources to a state of good whenever compliance drift is identified.

With the release of LPA Policy Generation, InsightCloudSec enables customers to take action when overly permissive roles or unused access is detected, automatically modifying the existing policy to align actual usage with granted permissions. Any actions that aren’t utilized over a 90-day period will be excluded from the new policy.

Permissions can’t become a point of friction for developers

In today’s world of continuous, fast-paced innovation, being able to move quickly and without friction is a key ingredient to delivering for customers and remaining competitive within our industries. Therefore, developers are often granted “godlike” access to leverage cloud services and build applications, in an effort to eliminate the potential that they will hit a roadblock later on. Peeling that back is a daunting task.

So how do you do that? Adopt the Principle of least privilege access, which recommends that a user should be given only those privileges needed for them to perform their function or task. If a user does not need a specific permission, the user should not have that permission.

Identity LPA requires dynamic assessment

The first step to executing on this initiative of LPA is to provide evidence to your dev teams that there is a problem to be solved. When first collaborating with your development partners, having a clear report of what permissions users have leveraged and what they have not can help move the discussion forward. If “Sam” has not used [insert permission] in the past 90 days, then does Sam really need this permission?

InsightCloudSec tracks permission usage and provides reporting over time of all your clouds, and is a handy tool to commence the discussion, laying the groundwork for continuous evaluation of the delta between used and unused permissions. This is critical, because while unused permissions may seem benign at first glance, they play a significant role in expanding your organization’s attack surface.

Effective cloud IAM requires prioritization

The continuous evaluation of cloud user activity compared to the permissions they have been previously granted will give security teams visibility into what permissions are going unused, as well as permissions that have been inappropriately escalated. This then provides a triggering point to investigate and ultimately enforce the principle of least privilege.

InsightCloudSec can proactively alert you to overly permissive access. This way security teams are able to continuously establish controls, and also respond to risk in real time based on suspicious activity or compliance drift.

Like with most security problems, prioritization is a key element to success. InsightCloudSec helps security teams prioritize which users to focus on by identifying which unused permissions pose the greatest risk based on business context. Not all permissions issues are equal from a risk perspective. For example, being able to escalate your privileges, exfiltrate data, or make modifications to security groups are privileged actions, and are often leveraged by threat actors when conducting an attack.

Taking action

Ultimately, you want to modify the policy of the user to match the user’s actual needs and access patterns. To ensure the insights derived from dynamically monitoring cloud access patterns and permissions are actionable, InsightCloudSec provides comprehensive reporting capabilities (JSON, report exports, etc.) that help streamline the response process to harden your IAM risk posture.

In an upcoming release, customers will be able to set up automation via “bots” to take immediate action on those insights. This will streamline remediation even further by reducing dependency on manual intervention, and in turn reduces the likelihood of human error.

When done right, LPA significantly reduces cloud risk

When done right, establishing and enforcing least-privilege access enables security teams to identify unused permissions and overly permissive roles and report them to your development teams. This is a key step in providing evidence of the opportunity to reduce an organization’s attack surface and risk posture. Minimizing the number of users that have been granted high-risk permissions to the ones that truly need them helps to reduce the blast radius in the event of a breach.

InsightCloudSec’s LPA Policy Remediation module is available today and leverages all your other cloud data for context and risk prioritization. If you’re interested in learning more about InsightCloudSec, and seeing how the solution can help your team detect and mitigate risk in your cloud environments, be sure to register for our bi-weekly demo series, which goes live every other Wednesday at 1pm EST.

Real-Time Risk Mitigation in Google Cloud Platform

Post Syndicated from Ben Austin original https://blog.rapid7.com/2022/10/12/real-time-risk-mitigation-in-google-cloud-platform/

Real-Time Risk Mitigation in Google Cloud Platform

With Google Cloud Next happening this week, there’s been some recent water cooler talk – okay, informal, ad hoc Zoom calls – where discussions about what makes Google Cloud Platform (GCP) unique when it comes to security. A few specific differences have popped up here and there (default data encryption, the way IAM is handled, etc.), but, generally speaking, many of the principles that apply to all other cloud providers apply to GCP environments.

For one, due to the speed and scale of these environments, it’s simultaneously very difficult and extremely critical to maintain an up-to-date inventory of the state of all resources in your environment. This means constantly monitoring your environment for resources being created, deleted, or modified in as close to real time as possible.

And in an effort to avoid ambiguity or hide behind marketing buzz terms, when I’m referring to “real time” here, I’m talking about sub 5-minute intervals based on activity happening in the environment. This is not to be confused with “near real time” approaches some vendors tout, which, in reality, still only pulls in data once or twice a day based on a static schedule.

In GCP, like in AWS, Azure, and all other cloud environments, simply getting a snapshot once a day to identify misconfigurations, vulnerabilities, or suspicious behaviors like you might with an on-prem data center just isn’t a scalable strategy. It’s a common cliche, but the ephemeral nature and rate of change in public cloud environments makes that kind of scanning strategy extremely ineffective when it comes to monitoring, analyzing, and eliminating actual risk in a cloud environment.

Let me lay out a couple examples where this kind of real-time monitoring can provide significant, potentially necessary, value to security teams working to make their cloud risk management programs more effective.

Identification of high-risk resources

As an example, say a developer is in a GCP project associated with your company’s revenue-generating application and they spin up a Cloud Storage instance that is, whether mistakenly or maliciously, open to the public internet.

If your security team is reliant on a scan to happen 12 hours later to get visibility into this activity, your organization will constantly be left open to significant risk. Take away the hyperbole here and assume it’s a much smaller risk or compliance violation. Even in that situation, your team is still working from behind and, presumably, almost always facing some level of stress about what issues are out there in the environment that they won’t know about for another 12-18 hours.

Worst of all, with this type of scanning you’re generally just getting a point-in-time snapshot of the environment and usually don’t know who made the change or how long ago it happened. This makes it much more difficult and time consuming for your team to actually assess the risk or get their hands on the right information to make an informed decision about how the situation should be addressed.

When a team is working with real-time data, however, they can be much more diligent and confident that they’re prioritizing the right issues at any given moment, with all the necessary context about who made the change and when it occurred. This not only helps teams stay ahead of issues and reduce the risk of a breach in their environment, but also helps keep individuals and teams feeling positive about the impact that the program is having on the organization.

Delayed remediation workflows

Building off of the previous example, it’s not only that teams can’t respond to risk they haven’t been notified of, it’s also that any automated response workflows your team may have built out to be more efficient are significantly less effective when they’re triggered by hours-old data. A 12-hour delay in an automation workflow all but eliminates the value of the automation itself, and it can actually cause headaches and confusion that detract from your team’s efficiency, rather than improving it (more on this in the next example).

In contrast, if you’re able to detect risky changes to your environment as they happen, you can automatically respond to that issue as it happens. In the case of this all being a mistake caused by a developer working a little too quickly, you’re able to automatically notify them of their error within a matter of minutes, likely while they’re still working within that project. Giving your development team this kind of feedback in the moment, rather than forcing them to context switch and go back into the project to fix the error a day later, is an excellent way to build stronger relationships and rapport with that team.

In the more rare case that this is indeed a malicious internal or external actor, enabling your automated remediation workflows to kick into gear within seconds and potentially stop the behavior could mean the difference between a minor incident and a breach requiring public disclosure from your organization.

Minimizing false positives and cross-team friction

Speaking of relationships with the development team (sorry, #DevSecOps), I can almost guarantee that working with data from scans or snapshots that occur every 12 or 24 hours in your cloud will cause friction between your two teams. Whether it’s tied to manual identification of risky resources or automated workflows notifying them of a non-compliant asset, working with stale data will inevitably lead to false positives that will both annoy and distract your already overburdened development team.

Take the example highlighted above, but instead, let’s say the developer actually spun up that Cloud Storage instance for a short amount of time in a dev instance with no actual customer data as part of a testing exercise. By the time your team gets visibility into this and either reaches out manually or has some automated notification sent to the developer, that instance could have already been deleted for hours. Now your team is looking at one set of old data and seeing an issue, meanwhile the developer is insisting that the storage container doesn’t even exist anymore. As mentioned above, this is going to cause headaches and frustration for both parties, and cause your team to lose credibility with the dev team.

At this point, you can probably guess where this is going next. With real-time monitoring in your environment this situation can be avoided altogether because your team will be looking at the same up-to-date information, and your team will be able to see that the storage container was shut down or removed from the project rather than spending time chasing down a false positive.

Earlier this month we released event-driven harvesting for GCP in InsightCloudSec. This agentless, real-time monitoring helps your security team achieve every one of the benefits outlined above while also avoiding API rate limiting. In addition, we’ve recently added GCP CIS Benchmarks v1.3.0, added GCP threat findings into our console, and added support for Google Directory to give visibility into IAM factors such as user last login, MFA status, group association and more.

If you want to learn more about how Rapid7 can help you secure Google Cloud Platform, or any other public cloud environment, sign up for our live bi-weekly demo of InsightCloudSec.

[Security Nation] Chris Levendis and Lisa Olson on Cloud CVEs

Post Syndicated from Rapid7 original https://blog.rapid7.com/2022/09/14/security-nation-chris-levendis-and-lisa-olson-on-cloud-cves/

[Security Nation] Chris Levendis and Lisa Olson on Cloud CVEs

In this episode of Security Nation, Jen and Tod chat with Chris Levendis of MITRE and Lisa Olson of Microsoft about assigning CVE IDs for vulnerabilities affecting cloud solutions. They recount their experiences working with the CVE board to establish guidelines for disclosing cloud vulnerabilities and talk through some of the challenges in understanding responsibility for mitigating and managing risks in the cloud.

Stick around for our Rapid Rundown, where Tod and Jen talk about a helpful new feature in iOS 16 that allows users to tell their devices to forget certain Wi-Fi networks, as well as RFC 9293, the newly dropped transmission control protocol (TCP) that obsoletes RFC 793.

Chris Levendis

[Security Nation] Chris Levendis and Lisa Olson on Cloud CVEs

Chris Levendis is a Principal Systems Engineer in the Cybersecurity Operations & Integration department in the Center for Securing the Homeland at MITRE. He has supported various DHS missions since 2004, including infrastructure protection and cybersecurity. Currently, in support of the Cybersecurity and Infrastructure Security Agency (CISA), Chris leads the Homeland Security Systems Engineering and Development Institute’s (HSSEDI) work for Threat Hunting, Office of the Chief Technology Officer (OCTO), Common Vulnerabilities and Exposures (CVE), Common Weakness Enumeration (CWE), and Common Attack Pattern Enumeration and Classification (CAPEC).  

Lisa Olson

[Security Nation] Chris Levendis and Lisa Olson on Cloud CVEs

Lisa Olson has been in the business of developing technology and products to manage complex networks and network devices since the 1980s. She started her career working as a software engineer for IBM and has gone on to management positions for large companies including Boeing and Jupiter/Media Metrix.

For the last 10 years, Lisa has immersed herself in cybersecurity by managing Microsoft’s monthly Security Update releases (aka Patch Tuesday). Under her leadership, Patch Tuesday has undergone digital transformation from a primarily manual labor-intensive production of security bulletins for a relatively small number of products, to a highly automated all-electronic environment supporting hundreds of products including Microsoft’s Azure via a database and APIs. The Security Update Guide is published by Lisa’s team every month and provides information about Microsoft’s CVE list.

Show notes

Interview links

Rapid Rundown links

Like the show? Want to keep Jen and Tod in the podcasting business? Feel free to rate and review with your favorite podcast purveyor, like Apple Podcasts.

Want More Inspiring Stories From the Security Community?

Subscribe to Security Nation Today

How a Principal Engineer Made His Journey to Cloud Security With Rapid7

Post Syndicated from Tal Avissar original https://blog.rapid7.com/2022/09/13/how-a-principal-engineer-made-his-journey-to-cloud-security-with-rapid7/

How a Principal Engineer Made His Journey to Cloud Security With Rapid7

The first programming language I learned in my childhood was Pascal. I was 12 years old at the time, and I quickly developed a passion for technology.

From a young age, I always knew I wanted to learn engineering and computer science. I wanted to solve big design and architecture problems while building new products that would influence the many people using software every day. The idea that we can use technology to build better tools inspires me, and I get excited about finding ways to help people work more efficiently.

Cybersecurity is such an interesting field because of the unique challenges and complexities associated with it. With my prior knowledge and background in security fundamentals and algorithms, joining Rapid7 felt like an exciting opportunity to grow my career.

An approachable start to a new challenge

Starting a role in a new industry can feel overwhelming, but Rapid7 has provided me the tools to make it a successful transition.

I joined Rapid7 as a Principal Engineer within our Cloud Security team. When I joined, I had some background in cybersecurity and security. Upon joining, I was immediately supported with the training programs and learning materials that helped me get up to speed and understand the business in more detail.

As a new hire, I had an excellent onboarding experience. The onboarding program gave me the chance to experience the unique culture and values of Rapid7, while also learning more about our industry, products, and the evolving needs of our customers. With the right tools, programs, and culture, I felt supported from day 1 to begin learning and immerse myself into the business and culture.

What sets Rapid7 apart

There are a lot of things that make Rapid7 unique as an employer. The people who work here are incredibly smart and kind, and the company places emphasis on learning and development, which shows they care about their people. It’s important for me to be in an environment where the business and leaders support their teams and care about giving them the right resources and tools they need to do the job, while also growing their own skills and knowledge. In engineering, the team gets access to the tools and tech stack requirements needed to fulfill our work.

Since I joined the company, I have experienced the reward of seeing the direct impact of my work. Being able to work autonomously to get the job done while having opportunities to mentor and coach others around me has been extremely rewarding. I love having the freedom to be creative, learn, and innovate new solutions. As I continue to grow within my career, I look forward to my next step in achieving my MSC degree in computer science. Being in an organization where I am creating products from scratch and using a cutting-edge tech stack helps contribute toward this goal.

I’ve learned a lot by taking a new step in my career and moving to a cloud security company. For those who are looking to do the same, I have a few pieces of advice to help you be successful:

  • Have an attitude of learning and growth.
  • There are many certifications you can get that will help introduce you to cloud technology. Check out certifications for GCP, AWS, and Azure to get comfortable.
  • Research and explore advanced concepts of security, encryption, and attack models. There is a lot of exciting activity happening in cybersecurity, and learning more about the industry can fuel your interest and help you understand the importance and impact your work in this field can have.

Interested in joining Tal on the Cloud Security team at Rapid7? Explore our open roles.

Additional reading:

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.

Integrating Cloud Security With DevOps and CI/CD Tools

Post Syndicated from Clint Merrill original https://blog.rapid7.com/2022/09/09/integrating-cloud-security-with-devops-and-ci-cd-tools/

Integrating Cloud Security With DevOps and CI/CD Tools

This is the latest post in our blog series on shifting left in cloud security. In our last post, we kicked off the series with a high-level overview about Rapid7’s approach to shifting cloud security into the application development lifecycle. For this post, we’ll dive into a key aspect of our approach: integrating cloud security with developer and DevOps tooling.

Incentivizing adoption by reducing friction

When integrating security into any part of the development lifecycle there are some important factors to consider, including the security tools you’ll integrate, the processes you’ll ask developers to follow, and how aggressively you intend to enforce certain policies. When making these decisions, it’s important to consider the goals of adopting DevOps practices and infrastructure as code (IaC) respectively: to improve the velocity of application development and delivery, and to empower development teams to provision cloud infrastructure resources on a self-service basis.  

Infusing security into these goals requires guardrails and routine checks to make sure the need for speed doesn’t create vulnerabilities or potentially exploitable misconfigurations. For IaC development, this is accomplished by having individual developers scan templates and plans as early as possible, and at key points in the CI/CD pipeline, before they’re considered for use in staging or production deployment. This is much easier said than done, as it relies on organizational buy-in, particularly from the developers who are typically laser-focused on bringing new products and features to market as fast as possible with the highest quality possible.

As with anything that relies on multiple teams collaborating in a process, the goal is to make it as easy as possible to adopt and demonstrate tangible value to all involved. Shifting security left into the software development lifecycle (SDLC) via developers and CI/CD tool integrations is a perfect application of this. One common example is allowing developers to execute scans on IaC templates or plans prior to a push or pull request, using a local command-line interface (CLI) tool.

The comfort of the CLI

In this context, a CLI tool allows a developer to interact with IaC security scanning features via a terminal prompt for familiarity and convenience. This comfortable experience will encourage adoption by using the CLI rather than engaging with a security product interface or API directly. In late 2021, we released our first CLI tool to initiate IaC scans in InsightCloudSec (ICS): mimics.

mimics has many intended uses that will expand over the time, but for now, the primary goals are:

  1. Enabling developers to execute on-demand security scans of their IaC plans and templates with results delivered directly in the CLI, thereby shortening the discovery and feedback loop for security and compliance issues to the point of immediate remediation
  2. Enabling DevOps teams to easily integrate IaC security scans at any point in the CI/CD workflow, thereby standardizing the process and enforcing security compliance checks and remediation as needed before progressing to the next integration or deployment step

In all cases, the mimics CLI simplifies integration and doesn’t require more costly script-based integration with the ICS API.  In some cases, unique IaC security capabilities are exclusively available via mimics.

Introducing GitHub Actions integration

InsightCloudSec recently launched a GitHub Action to facilitate a bidirectional integration with our IaC scanning feature. Our goal is to streamline the incorporation of IaC security scans into your cloud application CI/CD process governed by GitHub. If you’re not familiar with GitHub Actions, they allow you to automate, customize, and execute workflow steps, including security and compliance checks. In doing so, users can discover, create, and share Actions with other community members.

A great use of the mimics CLI is to integrate with GitHub using our Action to trigger an ICS IaC scan at defined points in your workflow. Upon completion of the scan, you’ll receive an overall pass/fail result in reply, as well as detailed findings, if any, in SARIF format for display in the GitHub Advanced Security module as security alerts. If you don’t subscribe to the GitHub Advance Security module, you can still trigger IaC security scans and receive an overall pass/fail result to govern the workflow step, plus a detailed findings report in one of various readable formats.

More DevOps tool integrations on the way

As you can see, Rapid7’s InsightCloudSec is meeting developers and DevOps teams where they are today and expanding in the near future. We want to make integrating security controls by development teams easier. And we aren’t stopping there. We have a deep roadmap of additional integrations that will be coming soon. However, it’s important to note that you’re not limited by our formal integrations. The mimics CLI makes your custom integrations a snap, and we have examples in our product documents.

We understand the profound impact shifting security left can have on organizational buy-in, overall team efficiency, and of course, cloud security outcomes. Keep an eye out for upcoming enhancements that will further help you seamlessly integrate security throughout the entire SDLC.

If you’re interested in learning more about how InsightCloudSec helps your team get contextualized insight into your cloud security and risk posture, be sure to check out our bi-weekly demo series Gaining Layered Context in Cloud Security, which goes live every other Wednesday at 1pm EST.

Additional reading:

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.

3 Ways to Improve Data Protection in the Cloud

Post Syndicated from Jesse Mack original https://blog.rapid7.com/2022/09/07/3-ways-to-improve-data-protection-in-the-cloud/

3 Ways to Improve Data Protection in the Cloud

Cloud complexity is now a well-documented and widely felt phenomenon across technology teams — IT, development, and security alike. Multi-cloud architectures have become the norm, with 89% of organizations embracing a strategy that involves multiple cloud vendors. Not only are companies managing greater amounts of data than ever before, they’re also spread across an ever-increasing array of cloud services, applications, and devices.

Securing all this information and preventing data loss in a multi-cloud environment would be a tall task for any security team. Add to the mix an increasingly heightened threat landscape and an ongoing cybersecurity skills shortage, and the challenge becomes even greater.

Rapid7, Mimecast, and Netskope recently published a joint white paper outlining best practices for cloud data protection and pinpointing some key resources that organizations can leverage in this effort. Here are three key concepts the paper highlights.

1. Embrace AI

Artificial intelligence (AI) and machine learning are well-known technologies at this point, but their potential is only just beginning to be tapped when it comes to helping security teams become more efficient and more effective.

Examples of AI-based tools that can help security teams include curated detections within an extended detection and response (XDR) platform, as well as intelligent threat and anomaly detection within cloud security tools.

Machine learning won’t ever replace the trained eye and keen insight of a veteran cybersecurity analyst — but AI-based tools can take on some of the repetitive and time-consuming tasks that security pros face, allowing analysts to increase productivity and focus on the alerts and issues that matter most. The goal is human-machine collaboration, with AI augmenting and boosting the capabilities of the analyst.

2. Utilize automation

Automation and AI work together as a one-two punch of process improvement for security. If an AI-based tool detects an anomalous event, automation allows you to set up actions that can take place in response to that suspicious activity. This can help get the ball rolling faster on mitigating security issues — and speed is the name of the game when it comes to keeping out attackers.

In the context of a cloud security platform, built-in automation and remediation tools let you create bots that can carry out certain tasks, specified by:

  • Scope: What resources the bot should evaluate — i.e., specific cloud resource groups, or certain types of resources contained in those groups
  • Filters: The conditions in which a bot should act — e.g., what tags the resource has, or whether the ports are open
  • Actions: What task you want the bot to carry out — e.g., delete a resource, start or stop an instance, or send an email with key information about the resource in question

3. Leverage integrations

AI and automation can help drive efficiencies — but with a multitude of cloud services in play, there’s a risk that these automated actions proliferate and become unwieldy, making it tough for security teams to reap the full benefits. This is where integrations become critical: They allow teams to coordinate actions quickly and seamlessly across multiple vendor systems.

Integrations make it easier to create a holistic security environment formed by a consistent set of controls, rather than a patchwork of best practices. For example, if you have an integration that links your email security gateway to your security information and event management (SIEM) tool, you can create an alert when a user receives an email containing suspected ransomware or malware, and take automated remediation actions instantly. Or if your security service edge (SSE) platform detects a serious data exfiltration risk, you can build a customized workflow in your security orchestration, automation, and response (SOAR) to quarantine that resource or take it offline.

Dive deeper on cloud data protection

Keeping data secure in the cloud comes with its share of challenges, but integrations that leverage AI-based analytics and automated workflows can help you ensure you know where your data is, what security controls are in place, and what threats there might be in your environment.

Looking to go deeper on how to bring this vision to life? Download the white paper today, or join experts from Mimecast, Netskope, and Rapid7 for the webinar “Data Protection and Control in the Cloud” at 2pm EST on Tuesday, September 13.

Additional reading:

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.

AWS re:Inforce 2022: Key announcements and session highlights

Post Syndicated from Marta Taggart original https://aws.amazon.com/blogs/security/aws-reinforce-2022-key-announcements-and-session-highlights/

AWS re:Inforce returned to Boston, MA, in July after 2 years, and we were so glad to be back in person with customers. The conference featured over 250 sessions and hands-on labs, 100 AWS partner sponsors, and over 6,000 attendees over 2 days. If you weren’t able to join us in person, or just want to revisit some of the themes, this blog post is for you. It summarizes all the key announcements and points to where you can watch the event keynote, sessions, and partner lightning talks on demand.

Key announcements

Here are some of the announcements that we made at AWS re:Inforce 2022.

Watch on demand

You can also watch these talks and learning sessions on demand.

Keynotes and leadership sessions

Watch the AWS re:Inforce 2022 keynote where Amazon Chief Security Officer Stephen Schmidt, AWS Chief Information Security Officer CJ Moses, Vice President of AWS Platform Kurt Kufeld, and MongoDB Chief Information Security Officer Lena Smart share the latest innovations in cloud security from AWS and what you can do to foster a culture of security in your business. Additionally, you can review all the leadership sessions to learn best practices for managing security, compliance, identity, and privacy in the cloud.

Breakout sessions and partner lightning talks

  • Data Protection and Privacy track – See how AWS, customers, and partners work together to protect data. Learn about trends in data management, cryptography, data security, data privacy, encryption, and key rotation and storage.
  • Governance, Risk, and Compliance track – Dive into the latest hot topics in governance and compliance for security practitioners, and discover how to automate compliance tools and services for operational use.
  • Identity and Access Management track – Hear from AWS, customers, and partners on how to use AWS Identity Services to manage identities, resources, and permissions securely and at scale. Learn how to configure fine-grained access controls for your employees, applications, and devices and deploy permission guardrails across your organization.
  • Network and Infrastructure Security track – Gain practical expertise on the services, tools, and products that AWS, customers, and partners use to protect the usability and integrity of their networks and data.
  • Threat Detection and Incident Response track – Learn how AWS, customers, and partners get the visibility they need to improve their security posture, reduce the risk profile of their environments, identify issues before they impact business, and implement incident response best practices.
  • You can also catch our Partner Lightning Talks on demand.

Session presentation downloads are also available on our AWS Event Contents page. Consider joining us for more in-person security learning opportunities by registering for AWS re:Invent 2022, which will be held November 28 through December 2 in Las Vegas. We look forward to seeing you there!

If you’d like to discuss how these new announcements can help your organization improve its security posture, AWS is here to help. Contact your AWS account team today.

 
If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, contact AWS Support.

Want more AWS Security news? Follow us on Twitter.

Author

Marta Taggart

Marta is a Seattle-native and Senior Product Marketing Manager in AWS Security Product Marketing, where she focuses on data protection services. Outside of work you’ll find her trying to convince Jack, her rescue dog, not to chase squirrels and crows (with limited success).

Author

Maddie Bacon

Maddie (she/her) is a technical writer for AWS Security with a passion for creating meaningful content. She previously worked as a security reporter and editor at TechTarget and has a BA in Mathematics. In her spare time, she enjoys reading, traveling, and all things Harry Potter.

No Damsels in Distress: How Media and Entertainment Companies Can Secure Data and Content

Post Syndicated from Ryan Blanchard original https://blog.rapid7.com/2022/08/08/no-damsels-in-distress-how-media-and-entertainment-companies-can-secure-data-and-content/

No Damsels in Distress: How Media and Entertainment Companies Can Secure Data and Content

Streaming is king in the media and entertainment industry. According to the Motion Picture Association’s Theatrical and Home Entertainment Market Environment Report, the global number of streaming subscribers grew to 1.3 billion in 2021. Consumer demand for immediate digital delivery is skyrocketing. Producing high-quality content at scale is a challenge media companies must step up to on a daily basis. One thing is for sure: Meeting these expectations would be unmanageable left to human hands alone.

Fortunately, cloud adoption has enabled entertainment companies to meet mounting customer and business needs more efficiently. With the high-speed workflow and delivery processes that the cloud enables, distributing direct-to-consumer is now the industry standard.

As media and entertainment companies grow their cloud footprints, they’re also opening themselves up to vulnerabilities threat actors can exploit — and the potential consequences can be financially devastating.

Balancing cloud security with production speed

In 2021, a Twitch data breach showed the impact cyberattacks can have on intellectual property at media and entertainment companies. Attackers stole 128 gigabytes of data from the popular streaming site and posted the collection on 4chan. The released torrent file contained:

  • The history of Twitch’s source code
  • Programs Twitch used to test its own vulnerabilities
  • Proprietary software development kits
  • An unreleased online games store intended to compete with Steam
  • Amazon Game Studios’ next title

Ouch. In mere moments, the attackers stole a ton of sensitive IP and a key security strategy. How did attackers manage this? By exploiting a single misconfigured server.

Before you think, “Well, that couldn’t happen to us,” consider that cloud misconfigurations are the most common source of data breaches.

Yet, media and entertainment businesses can’t afford to slow down their adoption and usage of public cloud infrastructure if they hope to remain relevant. Consumers demand timely content, whether it’s the latest midnight album drop from Taylor Swift or breaking news on the war in Ukraine.

Media and entertainment organizations must mature their cloud security postures alongside their content delivery and production processes to maintain momentum while protecting their most valuable resources: intellectual property, content, and customer data.

We’ve outlined three key cloud security strategies media and entertainment companies can follow to secure their data in the cloud.

1. Expand and consolidate visibility

You can’t protect what you can’t see. There are myriad production, technical, and creative teams working on a host of projects at a media and entertainment company – and they all interact with cloud and container environments throughout their workflow. This opens the door for potential misconfigurations (and then breaches) if these environments aren’t carefully tracked, secured, or even known about.

Here are some key considerations to make:

  • Do you know exactly what platforms are being used across your organization?
  • Do you know how they are being used and whether they are secure?

Most enterprises lack visibility into all the cloud and container environments their teams use throughout each step of their digital supply chain. Implementing a system to continuously monitor all cloud and container services gives you better insight into associated risks. Putting these processes into place will enable you to tightly monitor – and therefore protect – your growing cloud footprint.

How to get started: Improve visibility by introducing a plan for cloud workload protection.

2. Shift left to prevent risk earlier

Cloud, container, and other infrastructure misconfigurations are a major area of concern for most security teams. More than 30% of the data breaches studied in our 2022 Cloud Misconfigurations Report were caused by relaxed security settings and misconfigurations in the cloud. These misconfigurations are alarmingly common across industries and can cause critical exposures, as evidenced in the following example:

In 2021, a server misconfiguration on Sky.com (a UK-based media company) revealed access credentials to a production-level database and IP addresses to development endpoints. This meant that anyone with those released credentials or addresses could easily access a mountain of proprietary data from the Comcast subsidiary.

One way to avoid these types of breaches is to prevent misconfigurations in your Infrastructure as Code (IaC) templates. Scanning IaC templates, such as Terraform, reduces the likelihood of cloud misconfigurations by ensuring that any templates that are built and deployed are already vetted against the same security and compliance checks as your production cloud infrastructure and services.

By leveraging IaC scanning that provides fast, context-rich results to resource owners, media and entertainment organizations can build a stronger security foundation while reducing friction across DevOps and security teams and cutting down on the number of 11th-hour fixes. Solving problems in the CI/CD pipeline improves efficiency by correcting issues once rather than fixing them over and over again at runtime.

How to get started: Learn about the first step of shifting left with Infrastructure as Code in the CI/CD pipeline.

3. Create a culture of security

As the saying goes, a chain is only as strong as its weakest link. Cloud security practices won’t be as effective or efficient if an organization’s workforce doesn’t understand and value secure processes. A culture of collaboration between DevOps and security is a good start, but the entire organization must understand and uphold security best practices.

Fostering a culture that prioritizes the protection of digital content empowers all parts of (and people in) your supply chain to work with secure practices front-of-mind.

What’s the tell-tale sign that you’ve created a culture of security? When all employees, no matter their department or role, see it as simply another part of their job. This is obviously not to say that you need to turn all employees, or even developers, into security experts, but they should understand how security influences their role and the negative consequences to the business if security recommendations are avoided or ignored.

How to get started: Share this curated set of resources on cloud security for media and entertainment companies with your team.

Achieving continuous content security

Media and entertainment companies can’t afford to slow down if they hope to meet consumer demands. They can’t afford to neglect security, either, if they want to maintain consumer trust.

Remember, the ultimate offense is a strong defense. Building security into your cloud infrastructure processes from the beginning dramatically decreases the odds that an attacker will find a chink in your armor. Moreover, identifying and remediating security issues sooner plays a critical role in protecting consumer data and your intellectual property and other media investments.

Want to learn more about how media and entertainment companies can strengthen their cloud security postures?

Read our eBook: Protecting IP and Consumer Data in the Streaming Age: A Guide to Cloud Security for Digital Media & Entertainment.

Additional reading:

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.

Collaboration Drives Secure Cloud Innovation: Insights From AWS re:Inforce

Post Syndicated from Jesse Mack original https://blog.rapid7.com/2022/08/02/collaboration-drives-secure-cloud-innovation-insights-from-aws-re-inforce/

Collaboration Drives Secure Cloud Innovation: Insights From AWS re:Inforce

This year’s AWS re:Inforce conference brought together a wide range of organizations that are shaping the future of the cloud. Last week in Boston, cloud service providers (CSPs), security vendors, and other leading organizations gathered to discuss how we can go about building cloud environments that are both safe and scalable, driving innovation without sacrificing security.

This array of attendees looks a lot like the cloud landscape itself. Multicloud architectures are now the norm, and organizations have begun to search for ways to bring their lengthening lists of vendors together, so they can gain a more cohesive picture of what’s going on in their environment. It’s a challenge, to be sure — but also an opportunity.

These themes came to the forefront in one of Rapid7’s on-demand booth presentations at AWS re:Inforce, “Speeding Up Your Adoption of CSP Innovation.” In this talk, Chris DeRamus, VP of Technology – Cloud Security at Rapid7, sat down with Merritt Baer — Principal, Office of the CISO at AWS — and Nick Bialek — Lead Cloud Security Engineer at Northwestern Mutual — to discuss how organizations can create processes and partnerships that help them quickly and securely utilize new services that CSPs roll out. Here’s a closer look at what they had to say.

Building a framework

The first step in any security program is drawing a line for what is and isn’t acceptable — and for many organizations, compliance frameworks are a key part of setting that baseline. This holds true for cloud environments, especially in highly regulated industries like finance and healthcare. But as Merritt pointed out, what that framework looks like varies based on the organization.

“It depends on the shop in terms of what they embrace and how that works for them,” she said. Benchmarks like CIS and NIST can be a helpful starting point in moving toward “continuous compliance,” she noted, as you make decisions about your cloud architecture, but the journey doesn’t end there.

For example, Nick said he and his team at Northwestern Mutual use popular compliance benchmarks as a foundation, leveraging curated packs within InsightCloudSec to give them fast access to the most common compliance controls. But from there, they use multiple frameworks to craft their own rigorous internal standards, giving them the best of all worlds.

The key is to be able to leverage detective controls that can find noncompliant resources across your environment so you can take automated actions to remediate — and to be able to do all this from a single vantage point. For Nick’s team, that is InsightCloudSec, which provides them a “single engine to determine compliance with a single set of security controls, which is very powerful,” he said.

Evaluating new services

Consolidating your view of the cloud environment is critical — but when you want to bring on a new service and quickly evaluate it for risk, Merritt and Nick agreed on the importance of embracing collaboration and multiplicity. When it’s working well, a multicloud approach can allow this evaluation process to happen much more quickly and efficiently than a single organization working on their own.

“We see success when customers are embracing this deliberate multi-account architecture,” Merritt said of her experience working with AWS users.

At Northwest Mutual, Nick and his team use a group evaluation approach when onboarding a new cloud service. They’ll start the process with the provider, such as AWS, then ask Rapid7 to evaluate the service for risks. Finally, the Northwest Mutual team will do an assessment that pays close attention to the factors that matter most to them, like disaster recovery and identity and access management.

This model helps Nick and his team realize the benefits of the cloud. They want to be able to consume new services quickly so they can innovate at scale, but their team alone can’t keep up the work needed to fully vet each new resource for risks. They need a partner that can help them keep pace with the speed and elasticity of the cloud.

“You need someone who can move fast with you,” Nick said.

Automating at scale

Another key component of operating quickly and at scale is automation. “Reducing toil and manual work,” as Nick put it, is essential in the context of fast-moving and complex cloud environments.

“The only way to do anything at scale is to leverage automation,” Merritt insisted. Shifting security left means weaving it into all decisions about IT architecture and application development — and that means innovation and security are no longer separate ideas, but simultaneous parts of the same process. When security needs to keep pace with development, being able to detect configuration drift and remediate it with automated actions can be the difference between success and stalling out.

Plus, who actually likes repetitive, manual tasks anyway?

“You can really put a lot of emphasis on narrowing that gray area of human decision-making down to decisions that are truly novel or high-stakes,” Merritt said.

This leveling-up of decision-making is the real opportunity for security in the age of cloud, Merritt believes. Security teams get to be freed from their former role as “the shop of no” and instead work as innovators to creatively solve next-generation problems. Instead of putting up barriers, security in the age of cloud means laying down new roads — and it’s collaboration across internal teams and with external vendors that makes this new model possible.

Additional reading:

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.

Shift Left: Secure Your Innovation Pipeline

Post Syndicated from Ryan Blanchard original https://blog.rapid7.com/2022/08/01/shift-left-secure-your-innovation-pipeline/

Shift Left: Secure Your Innovation Pipeline

There’s no shortage of buzzwords in the tech world. Some are purely marketing spin. But others are colloquial ways for the industry to talk about complex topics that have a massive impact on how organizations and teams drive innovation and work more efficiently. Here at Rapid7, we believe the “shift left” movement very much falls in the latter category.

Because we see shifting left as so critical to an effective cloud security strategy, we’re kicking off a new blog series covering how organizations can seamlessly incorporate security best practices and technologies into their existing DevOps workflows — and, of course, how InsightCloudSec and the brilliant team here at Rapid7 can help.

What does “shift left” actually mean?

For those who might not be familiar with the term, “shift left” can be used interchangeably with DevOps methodologies. The idea is to “shift” tasks that have typically been performed by centralized and dedicated operations teams earlier in the software development life cycle (SDLC). In the case of security, this means weaving security guardrails and checks into development, fixing problems at the source rather than waiting to do so upon deployment or production.

Shift Left: Secure Your Innovation Pipeline

Historically, security was centered around applying checks and scanning for known vulnerabilities after software was built as part of the test and release processes. While this is an important step in the cycle, there are many instances in which this is too late to begin thinking about the integrity of your software and supporting infrastructure — particularly as organizations adopt DevOps practices, resources are increasingly provisioned declaratively, and the development cycle becomes a more iterative, continuous process.

Our philosophy on shift left

One of the most commonly cited concerns we hear from organizations attempting to shift left is the potential to create a bottleneck in development, as developers need to complete additional steps to clear compliance and security hurdles. This is a crucial consideration, given that accelerating software development and increasing efficiency is often the driving force behind adopting DevOps practices in the first place. Security must catch up to the pace of development, not slow it down.

Shift left is very much about decentralizing security to match the speed and scale of the cloud, and when done poorly, it can erode trust and be viewed as a gating factor to releasing high-quality code. This is what drives Rapid7’s fundamental belief that in order to effectively shift security left, you need to avoid adding friction into the process, and instead embrace the developer experience and meet devs where they are today.

How do you accomplish this? Here’s a few core concepts that we here at Rapid7 endorse:

Provide real-time feedback with clear remediation guidance

The main goal of DevOps is to accelerate the pace of software development and improve operating efficiency. In order to accomplish this without compromising quality and security, you must make sure that insights derived from your tooling are actionable and made available to the relevant stakeholders in real time. For instance, if an issue is detected in an IaC template, the developer should be immediately notified and provided with step-by-step guidance on how to fix the issue directly in the template itself.

Establish clear and consistent security and compliance standards

It’s important for an organization to have a clear and consistent definition of what “good” looks like. A well-centered definition of security and compliance controls helps establish a common standard for the entire organization, making measurement of compliance and risk easier to establish and report. Working from a single, centrally managed policy set makes it that much easier to ensure that teams are building compliant workloads from the start, and you can limit the time wasted repeatedly fixing issues after they reach production. A common standard for security that everyone is accountable for also establishes trust with the development community.

Integrate seamlessly with existing tool chains and processes

When adding any tools or additional steps into the development life cycle, it is critically important to integrate them with existing tools and processes to avoid adding friction and creating bottlenecks. This means that your security tools must be compatible with existing CI/CD tools (e.g., GitHub, Jenkins, Puppet, etc.) to make the process of scanning resources and remediating issues seamless, and to enable developers to complete their tasks without ever leaving the tools they are most comfortable working with.

Enable automation by shifting security left

Automation can be a powerful tool for teams managing sprawling and complex cloud environments. Shifting security left with IaC scanning allows you to catch faulty source templates before they’re ever used, allowing teams to leverage automation to deploy their cloud infrastructure resources with the confidence that they will align to organizational security standards.

Shifting cloud security left with IaC scanning

Infrastructure as code (IaC) refers to the ability to provision cloud infrastructure resources declaratively, by writing code in the same development environments used to write the software it is intended to support. IaC is a critical component of shifting left, as it empowers developers to write, test, and release software and infrastructure resources programmatically in a highly integrated process. This is typically done through pre-configured templates based on policies determined by operations teams, making development a shared and reproducible process.

When it comes to IaC security, we’re primarily talking about integrating the process of checking IaC templates to be sure that they won’t result in non-compliant infrastructure. But it shouldn’t stop there. In a perfect world, the IaC scanning tool will identify why a given template will be non-compliant, but it should also tell you how to fix it (bonus points if it can fix the problem for you!).

IaC scanning with InsightCloudSec

By this point, it should be clear that we here at Rapid7 strongly believe in incorporating security and compliance as early as possible in the development process, but we know this can be a daunting task. That’s why we built powerful capabilities into the InsightCloudSec platform to make integrating IaC scanning into your development workflows as easy and seamless as possible.

With IaC scanning in InsightCloudSec, your teams can identify and evaluate risk before infrastructure is ever built, stopping non-compliant or misconfigured resources from ever reaching production, and improving efficiency by fixing problems at the source once and for all, rather than repeatedly addressing them in runtime. With out-of-the-box support for popular IaC tools like Terraform and CloudFormation, InsightCloudSec provides teams with a common understanding of good that is consistent throughout the entire development life cycle.

Shifting security left requires consistency

Consistency is critical when shifting left, because if you’re scanning IaC templates with checks against policies that differ from those being applied in production, there’s a high likelihood that after some — likely short — period of time, those policy sets are going to drift, leading to missed vulnerabilities, misconfigurations, and/or non-compliant workloads. That may not seem like the end of the world, but it creates real problems for communicating issues across teams and increases the risk of inconsistent application of policies. When you lack consistency, it creates confusion among your stakeholders and erodes confidence in the effectiveness of your security program.

To address this, InsightCloudSec applies the same exact set of configuration standards and security policies across your entire CI/CD pipeline and even across your various cloud platforms (if your organization is one of the many that employ a hybrid cloud strategy). That means teams using IaC templates to provision infrastructure resources for their cloud-native applications can be confident they are deploying workloads that are in line with existing compliance and security standards — without having to apply a distinct set of checks, or cross-reference them with those being used in production environments.

Sounds amazing, right?! There’s a whole lot more that InsightCloudSec has to offer cloud security teams that we don’t have time to cover in this post, so follow this link if you’d like to learn more.

Additional reading:

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.

[VIDEO] An Inside Look at AWS re:Inforce 2022 From the Rapid7 Team

Post Syndicated from Jesse Mack original https://blog.rapid7.com/2022/07/29/video-an-inside-look-at-aws-re-inforce-2022-from-the-rapid7-team/

[VIDEO] An Inside Look at AWS re:Inforce 2022 From the Rapid7 Team

The summer of conferences rolls on for the cybersecurity and tech community — and for us, the excitement of being able to gather in person after two-plus years still hasn’t worn off. RSA was the perfect kick-off to a renewed season of security together, and we couldn’t have been happier that our second big stop on the journey, AWS re:Inforce, took place right in our own backyard in Boston, Massachusetts — home not only to the Rapid7 headquarters but also a strong and vibrant community of cloud, security, and other technology pros.

We asked three of our team members who attended the event — Peter Scott, VP Strategic Enablement – Cloud Security; Ryan Blanchard, Product Marketing Manager – InsightCloudSec; and Megan Connolly, Senior Security Solutions Engineer — to answer a few questions and give us their experience from AWS re:Inforce 2022. Here’s what they had to say.

What was your most memorable moment from AWS re:Inforce this year?


[VIDEO] An Inside Look at AWS re:Inforce 2022 From the Rapid7 Team

What was your biggest takeaway from the conference? How will it shape the way you think about cloud and cloud security practices in the months to come?


[VIDEO] An Inside Look at AWS re:Inforce 2022 From the Rapid7 Team

Thanks to everyone who came to say hello and talk cloud with us at AWS re:Inforce. We hope to see the rest of you in just under two weeks at Black Hat 2022 in Las Vegas!

Additional reading:

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.

Rapid7 at AWS re:Inforce: 2 Big Announcements

Post Syndicated from Aaron Sawitsky original https://blog.rapid7.com/2022/07/26/rapid7-at-aws-re-inforce-2-big-announcements/

Rapid7 at AWS re:Inforce: 2 Big Announcements

This year’s AWS re:Inforce conference in Boston has been jam-packed with thrilling speakers, deep insights on all things cloud, and some much-needed in-person collaboration from all walks of the technology community. It also coincides with some exciting announcements from AWS — and we’re honored to be a part of two of them. Here’s a look at how Rapid7 is building on our existing partnership with Amazon Web Services to help organizations securely advance in today’s cloud-native business landscape.

InsightIDR awarded AWS Security Competency

For seven years, AWS has issued security competencies to partners who have a proven track record of helping customers secure their AWS environments. Today at re:Inforce, AWS re-launched their Security Competency program, so that it better aligns with customers’ constantly evolving security challenges. Rapid7 is proud to be included in this re-launch, having obtained a security competency under the new criteria for its InsightIDR solution in the Threat Detection and Response category. This is Rapid7’s second AWS security competency and fourth AWS competency.

This designation recognizes that InsightIDR has demonstrated and successfully met AWS’s technical and quality requirements for providing customers with a deep level of software expertise in security incident and event management (SIEM), helping them achieve their cloud security goals.

InsightIDR integrates with a number of AWS services, including CloudTrail, GuardDuty, S3, VPC Traffic Mirroring, and SQS. InsightIDR’s UEBA feature includes dedicated AWS detections. The Insight Agent can be installed on EC2 instances for continuous monitoring. InsightIDR also features an out-of-the-box honeypot purpose-built for AWS environments. Taken together, these integrations and features give AWS customers the threat detection and response capabilities they need, all in a SaaS solution that can be deployed in a matter of weeks.

Adding another competency to Rapid7’s repertoire reaffirms our commitment to giving organizations the tools they need to innovate securely in a cloud-first world.

Rapid7 named a launch partner for AWS GuardDuty Malware Protection

Malware Protection is the new malware detection capability AWS has added to their GuardDuty service — and we’re honored to join them as a launch partner, with two products that support this new GuardDuty functionality.

GuardDuty is AWS’s threat detection service. It monitors AWS environments for suspicious behavior. Malware Protection introduces a new type of detection capability to GuardDuty. When GuardDuty fires an alert that’s related to an Amazon Elastic Cloud Compute (EC2) instance or a container running on EC2, Malware Protection will automatically run a scan on the instance in question and detect malware using machine learning and threat intelligence. When trojans, worms, rootkits, crypto miners, or other forms of malware are detected, they appear as new findings in GuardDuty, so security teams can take the right remediation actions.

Rapid7 customers can ingest GuardDuty findings (including the new malware detections) into InsightIDR and InsightCloudSec. In InsightIDR, each type of GuardDuty finding can be treated as a notable behavior or as an alert which will automatically trigger a new investigation. This allows security teams to know the instant suspicious activity is detected in their AWS environment and react accordingly. Should an investigation be triggered, teams can use InsightIDR’s native automation capabilities to enrich the data from GuardDuty, quarantine a user, and more. In the case where GuardDuty detects malware, teams can pull additional data from the Insight agent and even terminate malicious processes. In addition, customers can use InsightIDR’s Dashboards capability to keep an eye on GuardDuty and spot trends in the findings.

InsightCloudSec customers can likewise build automated bots that automatically react to GuardDuty findings. When GuardDuty has detected malware, a customer might configure a bot that terminates the infected instance. Alternatively, a customer might choose to reconfigure the instance’s security group to effectively isolate it while the team investigates. The options are practically endless.

Rapid7 and AWS continue to deepen partnership to protect your cloud workloads

AWS re:Inforce 2022 provides a welcome opportunity for the community to come together and share insights about managing and securing cloud environments, and we can’t think of better timing to announce these two areas of partnership with AWS. Click here to learn more about what we’re up to at this year’s AWS re:Inforce conference in Boston.

Additional reading:

NEVER MISS A BLOG

Get the latest stories, expertise, and news about security today.

What We’re Looking Forward to at AWS re:Inforce

Post Syndicated from Jesse Mack original https://blog.rapid7.com/2022/07/25/what-were-looking-forward-to-at-aws-re-inforce/

What We’re Looking Forward to at AWS re:Inforce

AWS re:Inforce 2022 starts tomorrow — Tuesday, July 26th — and we couldn’t be more excited to gather with the tech, cloud, and security communities in our home city of Boston. Here’s a sneak peek of the highlights to come at re:Inforce and what we’re looking forward to the most this Tuesday and Wednesday.

Expert insights at the Rapid7 booth

After two and half years of limited in-person gatherings, we have kind of a lot to say. That’s why we’re making the Rapid7 booth at AWS re:Inforce a hub for learning and sharing from our cybersecurity experts. Stop by and learn how our team members are tackling a range of topics in cloud and security overall, including:

  • Adapting Your VM Program for Cloud-Native Environments — Jimmy Green, VP of Software Engineering for Cloud, will walk through some of the key considerations when building a fully cloud-first approach to vulnerability management.
  • Speeding Up Your Adoption of CSP Innovation — Chris DeRamus, VP of Technology – Cloud, will detail how Rapid7 evaluates cloud service providers (CSPs) for risk in order to promote faster, more secure adoption.
  • Context Is King: The Future of Cloud Security Operations — Peter Scott, VP of Strategic Engagement for Cloud Security, will discuss why obtaining context around security data is key to managing complexity in cloud environments.
  • Hybrid Is Here: Is Your SOC Ready? — Megan Connolly, Senior Security Solutions Engineer, will highlight the role that extended detection and response (XDR) technology can play in helping SOCs move toward a cloud-first model.
  • InsightCloudSec Demo — Joe Brumbley, Cloud Security Solutions Engineer, and Sean Healy, Senior Domain Engineer – Enterprise Cloud Security, will show InsightCloudSec in action, taking you through the different use cases and features that enable integrated security for multi-cloud environments.

Sharing how we walk the walk

At Rapid7, we’re laser-focused on helping companies accelerate in the cloud without compromising security. Our technology and expertise help security teams bring that vision to life — and they form the foundation for how we secure our own cloud infrastructure, too.

In the AWS re:Inforce featured session, “Walking the Walk: AWS Security at Rapid7,” Ulrich Dangle (Director, Software Engineering – Platform) and Lauren Clausen Fenton (Manager, Software Engineering – Platform) will share their firsthand experiences developing, scaling, and operationalizing a cloud security program at Rapid7. They’ll talk about how they manage to reduce risk while supporting Rapid7’s business goals, as well as the needs of our fast-moving DevOps team.

Join us on Tuesday, July 26th, at 11:40 AM, or Wednesday, July 27th, at 10:05 AM to learn how our security team is working around-the-clock to keep our large cloud environment secure and compliant, with standardized configurations and a tried-and-true threat response playbook.

Conversations over cloudy beers

It’s no secret that great craft beer is an integral part of tech culture — so where better to talk about all things cloud than a Boston brewery known for the cloudy appearance of its hazy New England IPAs?

On Tuesday, July 26th, from 5:15 PM to 8 PM, we’ll be at Rapid7 Reception at Trillium Fort Point, right in the heart of the Seaport District. It’s a perfect chance to network with your fellow protectors and meet some of our Rapid7 security experts over a double dry-hopped pale ale or a nitro milk stout. (If beer’s not your thing, not to worry — we’ll have wine and seltzer, too.)

If that wasn’t enough…

Last but not least, we’re giving away a vacation of your choice valued at $5,000! The more you engage with us at re:Inforce, the more chances you have to win. You’ll be entered in the drawing when you stop by to see us at Booth 206 to receive a demo or watch a presentation, or when you attend the Rapid7 Reception at Trillium Fort Point.

Check out what we have planned and register with us today!